

Page 1
®
©Copyright 2008. All Rights Reserved
User Manual
Product Model:
xStack® DES-3500 Series
Layer 2 Managed Stackable Fast Ethernet Switch
Release 5.1
Page 2
ii
__________________________________________________________________________________
Information in this document is subject to change without notice.
© 2008 D-Link Corporation. All rights reserved.
Reproduction in any manner whatsoever without the written permission of D-Link Corporation is strictly forbidden.
Trademarks used in this text: D-Link and the D-LINK logo are trademarks of D-Link Corporation; Microsoft and Windows are registered trademarks of Microsoft
Corporation.
Other trademarks and trade names may be used in this document to refer to either the entities claiming the marks and names or their products. D-Link Corporation
disclaims any proprietary interest in trademarks and trade names other than its own.
July 2008
Page 3
Table of Contents
Preface ..............................................................................................................................................................................................viii
Intended Readers.................................................................................................................................................................................ix
Typographical Conventions..........................................................................................................................................................ix
Notes, Notices, and Cautions..............................................................................................................................................................ix
Safety Instructions ...............................................................................................................................................................................x
Safety Cautions.............................................................................................................................................................................. x
General Precautions for Rack-Mountable Products......................................................................................................................xi
Protecting Against Electrostatic Discharge..................................................................................................................................xii
Introduction..........................................................................................................................................................................................1
Switch Description......................................................................................................................................................................... 1
Features.......................................................................................................................................................................................... 1
Ports ............................................................................................................................................................................................... 2
Front-Panel Components................................................................................................................................................................ 2
LED Indicators............................................................................................................................................................................... 3
Rear Panel Description................................................................................................................................................................... 4
Side Panel Description................................................................................................................................................................... 4
Gigabit Combo Ports...................................................................................................................................................................... 5
Installation ...........................................................................................................................................................................................7
Package Contents........................................................................................................................................................................... 7
Before You Connect to the Network.............................................................................................................................................. 7
Installing the Switch without the Rack...........................................................................................................................................8
Installing the Switch in a Rack....................................................................................................................................................... 9
Mounting the Switch in a Standard 19" Rack..............................................................................................................................10
Power On (AC Power)..................................................................................................................................................................................11
Power Failure .................................................................................................................. ..............................................................................11
Connecting DC Power to DES-3526DC...................................................................................................................................... 11
Connecting the Switch....................................................................................................................................................................... 12
Switch to End Node ..................................................................................................................................................................... 12
Switch to Hub or Switch..............................................................................................................................................................13
Connecting To Network Backbone or Server .............................................................................................................................. 14
Introduction to Switch Management.................................................................................................................................................. 15
Management Options.........................................................................................................................................................................15
Web-based Management Interface............................................................................................................................................... 15
SNMP-Based Management.......................................................................................................................................................... 15
Connecting the Console Port (RS-232 DCE)............................................................................................................................... 15
First Time Connecting to the Switch............................................................................................................................................ 17
Password Protection..................................................................................................................................................................... 17
SNMP Settings............................................................................................................................................................................. 19
Page 4
Traps.............................................................................................................................................................................................................19
MIBs.............................................................................................................................................................................................................19
IP Address Assignment................................................................................................................................................................ 20
Connecting Devices to the Switch ............................................................................................................................................... 21
Web-based Switch Configuration...................................................................................................................................................... 22
Introduction........................................................................................................................................................................................22
Login to Web Manager................................................................................................................................................................ 22
Web-based User Interface............................................................................................................................................................ 23
Areas of the User Interface ...........................................................................................................................................................................23
Web Pages.................................................................................................................................................................................... 24
Configuring the Switch...................................................................................................................................................................... 25
Switch Information............................................................................................................................................................................26
IP Address.......................................................................................................................................................................................... 26
Advanced Settings .............................................................................................................................................................................30
Port Configuration .............................................................................................................................................................................32
Port Description................................................................................................................................................................................. 34
Port Mirroring....................................................................................................................................................................................35
Link Aggregation...............................................................................................................................................................................36
Understanding Port Trunk Groups................................................................................................................................................................36
LACP Port Setting.............................................................................................................................................................................39
MAC Notification.............................................................................................................................................................................. 40
MAC Notification Global Settings............................................................................................................................................... 40
MAC Notification Port Settings................................................................................................................................................... 41
IGMP .................................................................................................................................................................................................42
IGMP Snooping ........................................................................................................................................................................... 42
Static Router Ports Entry.............................................................................................................................................................. 44
Forbidden Router Ports Entry......................................................................................................................................................45
IGMP Multicast VLAN................................................................................................................................................................ 46
Spanning Tree....................................................................................................................................................................................49
802.1s MSTP ................................................................................................................................................................................................49
802.1w Rapid Spanning Tree ........................................................................................................................................................................49
Port Transition States....................................................................................................................................................................................49
Edge Port.......................................................................................................................................................................................................50
P2P Port........................................................................................................................................................................................................50
802.1d/802.1w/802.1s Compatibility............................................................................................................................................................50
STP Bridge Global Settings.........................................................................................................................................................51
MST Configuration Table............................................................................................................................................................ 54
MSTI Settings..............................................................................................................................................................................56
STP Instance Settings................................................................................................................................................................... 57
MSTP Port Information................................................................................................................................................................59
Loopback Detection...........................................................................................................................................................................62
Forwarding Filtering.......................................................................................................................................................................... 63
Page 5
Unicast Forwarding...................................................................................................................................................................... 63
Multicast Forwarding................................................................................................................................................................... 64
Multicast Port Filtering Mode...................................................................................................................................................... 65
VLANs...............................................................................................................................................................................................67
Understanding IEEE 802.1p Priority.............................................................................................................................................................67
VLAN Description....................................................................................................................................................................... 67
Notes about VLANs on the xStack
®
DES-3500 Series switches ..................................................................................................................67
IEEE 802.1Q VLANs................................................................................................................................................................... 67
802.1Q VLAN Tags......................................................................................................................................................................................69
Port VLAN ID...............................................................................................................................................................................................69
Tagging and Untagging.................................................................................................................................................................................70
Ingress Filtering............................................................................................................................................................................................70
Default VLANs.............................................................................................................................................................................................70
Port-based VLANs........................................................................................................................................................................................71
VLAN Segmentation.....................................................................................................................................................................................71
Asymmetric VLANs.....................................................................................................................................................................................72
VLAN and Trunk Groups .............................................................................................................................................................................73
Static VLAN Entry....................................................................................................................................................................... 73
GVRP Setting............................................................................................................................................................................... 76
Traffic Control ............................................................................................................................................................................. 77
Port Security................................................................................................................................................................................. 81
QoS....................................................................................................................................................................................................82
Advantages of QoS.......................................................................................................................................................................................82
Understanding QoS....................................................................................................................................................................................... 83
Port Bandwidth ............................................................................................................................................................................ 84
Scheduling.................................................................................................................................................................................... 85
802.1p Default Priority.................................................................................................................................................................86
802.1p User Priority..................................................................................................................................................................... 86
Traffic Segmentation.................................................................................................................................................................... 87
System Severity Alerts.......................................................................................................................................................................88
System Log Server............................................................................................................................................................................. 88
SNTP Settings.................................................................................................................................................................................... 90
Time Setting................................................................................................................................................................................. 90
Time Zone and DST..................................................................................................................................................................... 91
ACL ...................................................................................................................................................................................................93
Access Profile Table .................................................................................................................................................................... 93
ACL Flow Meter..............................................................................................................................................................................111
CPU Interface Filtering.................................................................................................................................................................... 112
CPU Interface Filtering Profile Table........................................................................................................................................112
Time Range Settings........................................................................................................................................................................123
IP-MAC Binding..............................................................................................................................................................................123
ACL Mode ................................................................................................................................................................................. 123
Page 6
IP-MAC Binding Port................................................................................................................................................................126
IP-MAC Binding Table.............................................................................................................................................................. 127
IP-MAC Binding Blocked.......................................................................................................................................................... 128
DHCP Snooping Entries ............................................................................................................................................................ 128
IP-MAC Binding Permit IP Pool............................................................................................................................................... 129
Limited IP Multicast Range............................................................................................................................................................. 130
Limited IP Multicast Range Profile Settings.............................................................................................................................. 130
Limited IP Multicast Range Status Setting................................................................................................................................ 131
Limited IP Multicast Range Setting........................................................................................................................................... 132
Layer 3 IP Networking.....................................................................................................................................................................133
Static ARP Table........................................................................................................................................................................ 133
Gratuitous ARP Settings..................................................................................................................................................................134
DHCP/BOOTP Relay................................................................................................................................................................. 135
DHCP / BOOTP Relay Global Settings......................................................................................................................................................135
The Implementation of DHCP Information Option 82 in the xStack
®
DES-3500 Series switches.............................................................137
DHCP/BOOTP Relay Interface Settings.....................................................................................................................................................138
DHCP Option 60 Settings...........................................................................................................................................................................139
DHCP Option 61 Settings...........................................................................................................................................................................140
DHCP Local Relay Settings........................................................................................................................................................................141
LLDP ...............................................................................................................................................................................................142
LLDP Global Settings................................................................................................................................................................ 142
Basic LLDP Port Settings .......................................................................................................................................................... 144
802.1 Extension LLDP Port Settings.........................................................................................................................................145
802.3 Extension LLDP Port Settings.........................................................................................................................................146
LLDP Management Address Settings........................................................................................................................................ 147
LLDP Statistics.......................................................................................................................................................................... 148
LLDP Management Address Table............................................................................................................................................ 149
LLDP Local Port Table.............................................................................................................................................................. 149
LLDP Remote Port Information................................................................................................................................................. 152
Security Management......................................................................................................................................................................153
Trusted Host.....................................................................................................................................................................................153
User Accounts.................................................................................................................................................................................. 154
Port Access Entity (802.1X)............................................................................................................................................................156
802.1x Port-Based and MAC-Based Access Control................................................................................................................. 156
Authentication Server .................................................................................................................................................................................157
Authenticator .............................................................................................................................................................................................. 157
Client...........................................................................................................................................................................................................158
Authentication Process............................................................................................................................................................... 158
Port-Based Network Access Control..........................................................................................................................................159
MAC-Based Network Access Control.......................................................................................................................................160
Configure Authenticator............................................................................................................................................................. 161
PAE System Control.................................................................................................................................................................. 164
Page 7
Port Capability............................................................................................................................................................................................164
Initializing Ports for Port Based 802.1x......................................................................................................................................................165
Initializing Ports for MAC Based 802.1x....................................................................................................................................................166
Reauthenticate Port(s) for Port Based 802.1x.............................................................................................................................................166
Reauthenticate Port(s) for MAC Based 802.1x...........................................................................................................................................167
RADIUS Server ......................................................................................................................................................................... 167
Guest VLANs............................................................................................................................................................................. 168
Limitations Using the Guest VLAN............................................................................................................................................................168
Guest VLAN Configuration....................................................................................................................................................... 169
Access Authentication Control........................................................................................................................................................169
Policy & Parameters................................................................................................................................................................... 171
Application's Authentication Settings........................................................................................................................................ 171
Authentication Server Group ..................................................................................................................................................... 172
Authentication Server Hosts....................................................................................................................................................... 173
Login Method Lists.................................................................................................................................................................... 175
Enable Method Lists .................................................................................................................................................................. 176
Local Enable Password..............................................................................................................................................................178
Enable Admin ............................................................................................................................................................................ 178
Secure Socket Layer (SSL)..............................................................................................................................................................180
Download Certificate.................................................................................................................................................................180
Configuration.............................................................................................................................................................................181
Secure Shell (SSH) ..........................................................................................................................................................................182
SSH Configuration..................................................................................................................................................................... 182
SSH Algorithm........................................................................................................................................................................... 183
SSH User Authentication........................................................................................................................................................... 185
SNMP Manager ...............................................................................................................................................................................187
SNMP Settings........................................................................................................................................................................... 187
Traps...........................................................................................................................................................................................................187
MIBs...........................................................................................................................................................................................................187
SNMP User Table......................................................................................................................................................................188
SNMP View Table..................................................................................................................................................................... 190
SNMP Group Table.................................................................................................................................................................... 191
SNMP Community Table........................................................................................................................................................... 192
SNMP Host Table......................................................................................................................................................................193
SNMP Engine ID....................................................................................................................................................................... 194
SNMP Trap................................................................................................................................................................................194
Safeguard Engine ............................................................................................................................................................................. 196
Filter................................................................................................................................................................................................. 198
DHCP Server Screening Setting ................................................................................................................................................ 198
DHCP Client Filtering Setting ................................................................................................................................................... 199
NetBIOS Filtering Setting.......................................................................................................................................................... 200
CPU Filtering Settings ............................................................................................................................................................... 202
Page 8
ARP Spoofing Prevention.......................................................................................................................................................... 202
Monitoring.......................................................................................................................................................................................204
Port Utilization.................................................................................................................................................................................204
CPU Utilization................................................................................................................................................................................205
Memory Usage.................................................................................................................................................................................205
Packets.............................................................................................................................................................................................207
Received (RX)............................................................................................................................................................................ 207
UMB Cast (RX).........................................................................................................................................................................208
Transmitted (TX) ....................................................................................................................................................................... 211
Errors ...............................................................................................................................................................................................213
Received (RX)............................................................................................................................................................................ 213
Transmitted (TX) ....................................................................................................................................................................... 215
Size - Packet Size............................................................................................................................................................................. 216
MAC Address..................................................................................................................................................................................219
Switch History Log..........................................................................................................................................................................220
IGMP Snooping Group.................................................................................................................................................................... 221
IGMP Snooping Forwarding............................................................................................................................................................222
VLAN Status....................................................................................................................................................................................223
Router Port....................................................................................................................................................................................... 223
Port Access Control.........................................................................................................................................................................223
Authenticator State..................................................................................................................................................................... 224
Layer 3 Features...............................................................................................................................................................................226
Browse ARP Table..................................................................................................................................................................... 226
Safeguard Engine Status..................................................................................................................................................................227
Cable Diagnostic.............................................................................................................................................................................. 228
Maintenance..................................................................................................................................................................................... 229
TFTP Services..................................................................................................................................................................................229
Download Firmware...................................................................................................................................................................229
Download Configuration File..................................................................................................................................................... 230
Upload Configuration................................................................................................................................................................. 230
Upload Log ................................................................................................................................................................................ 231
Multiple Image Services..................................................................................................................................................................231
Firmware Information................................................................................................................................................................ 231
Config Firmware Image............................................................................................................................................................. 232
Ping Test..........................................................................................................................................................................................233
Save Changes................................................................................................................................................................................... 233
Reset ................................................................................................................................................................................................ 234
Reset System.................................................................................................................................................................................... 234
Reset Config .................................................................................................................................................................................... 235
Reboot Device..................................................................................................................................................................................235
Logout.............................................................................................................................................................................................. 235
Page 9
D-Link Single IP Management........................................................................................................................................................ 236
Single IP Management (SIM) Overview..........................................................................................................................................236
The Upgrade to v1.6....................................................................................................................................................................................237
SIM Using the Web Interface ..........................................................................................................................................................238
Topology.......................................................................................................................................................................................... 239
Tool Tips.......................................................................................................................................................................................... 241
Right-Click................................................................................................................................................................................. 242
Group Icon..................................................................................................................... .............................................................................242
Commander Switch Icon.............................................................................................................................................................................243
Member Switch Icon...................................................................................................................................................................................244
Candidate Switch Icon................................................................................................................................................................................245
Menu Bar ................................................................................................................................................................................... 247
Group..........................................................................................................................................................................................................247
Device.........................................................................................................................................................................................................247
View............................................................................................................................................................................................................247
Firmware Upgrade ..................................................................................................................................................................... 248
Configuration File Backup/Restore............................................................................................................................................ 248
Upload Log File......................................................................................................................................................................... 248
Technical Specifications.................................................................................................................................................................. 250
Cables and Connectors.....................................................................................................................................................................252
System Log Entries..........................................................................................................................................................................253
Cable Lengths..................................................................................................................................................................................264
Mitigating ARP Spoofing Attacks Using Packet Content ACL.......................................................................................................265
Glossary........................................................................................................................................................................................... 273
Warrenties/Registration ...................................................................................................................................................................276
Tech Support.................................................................................................................................................................................... 284
Page 10
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
viii
Preface
The DES-3500 Series Manual is divided into sections that describe the system installation and operating instructions with
examples.
Section 1, Introduction - Describes the Switch and its features.
Section 2, Installation- Helps you get started with the basic installation of the Switch and also describes the front panel, rear
panel, side panels, and LED indicators of the Switch. Included in this section is a description of how to hook up the DC power
supply for the DES-3500 Series switches.
Section 3, Connecting the Switch - Tells how you can connect the Switch to your Ethernet/Fast Ethernet network.
Section 4, Introduction to Switch Management - Introduces basic Switch management features, including password
protection, SNMP settings, IP address assignment and connecting devices to the Switch.
Section 5, Introduction to Web-based Switch Management - Talks about connecting to and using the Web-based switch
management feature on the Switch.
Section 6, Configuring the Switch - A detailed discussion about configuring some of the basic functions of the Switch,
including accessing the Switch information, using the Switch's utilities and setting up network configurations, such as Quality
of Service, The Access Profile Table, port mirroring and configuring the Spanning Tree.
Section 7, Security Management - A discussion of the security features of the Switch, including Security IP, User Accounts,
Access Authentication Control, and SNMP.
Section 8, Monitoring - Features graphs and screens used in monitoring features an d pa ckets on the Switch.
Section 9, Maintenance - Features information on Switch utility functions, including TFTP Services, Switch History, Ping Test
Save Changes and Rebooting Services.
Section 10, Single IP Management - Discussion on the Single IP Management function of the Switch, including functions and
features of the Java based user interface and the utilities of the SIM function.
Appendix A, Technical Specifications - The technical specifications of the DES-3500 Series switches.
Appendix B, Cables and Connectors - Describes the RJ-45 receptacle/connector, straight through and crossover cables and
standard pin assignments.
Appendix C, Cable Lengths - Information on cable types and maximum distances.
Glossary - Lists definitions for terms and acronyms used in this document.
Page 11
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
ix
Intended Readers
The DES-3500 Manual contains information for setup and management of the Switch. This manual is intended for network
managers familiar with network management concepts and terminology.
Typographical Conventions
Convention Description
[ ]
In a command line, square brackets indicate an optional entry. For example: [copy
filename] means that optionally you can type copy followed by the name of the file. Do not
type the brackets.
Bold font
Indicates a button, a toolbar icon, menu, or menu item. For example: Open the File menu
and choose Cancel. Used for emphasis. May also indicate system messages or prompts
appearing on your screen. For example: You have mail. Bold font is also used to
represent filenames, program names and commands. For example: use the copy
command.
Boldface
Typewriter Font
Indicates commands and responses to prompts that must be typed exactly as printed in
the manual.
Initial capital letter
Indicates a window name. Names of keys on the keyboard have initial capitals. For
example: Click Enter.
Italics
Indicates a window name or a field. Also can indicate a variables or parameter that is
replaced with an appropriate word or string. For example: type filename means that you
should type the actual filename instead of the word shown in italic.
Menu Name > Menu
Option
Menu Name > Menu Option Indicates the menu structure. Device > Port > Port
Properties means the Port Properties menu option under the Port menu option that is
located under the Device menu.
Notes, Notices, and Cautions
A NOTE indicates important information that helps you make better use of your device.
A NOTICE indicates either potential damage to hardware or loss of data and tells you
how to avoid the problem.
A CAUTION indicates a potential for property damage, personal injury, or death.
Page 12
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
x
Safety Instructions
Use the following safety guidelines to ensure your own personal safety and to help protect your system from potential damage.
Throughout this document, the caution icon ( ) is used to indicate cautions and precautions that you need to review and follow.
Safety Cautions
To reduce the risk of bodily injury, electrical shock, fire, and damage to the equipment, observe the following precautions.
• Observe and follow service markings.
• Do not service any product except as explained in your system documentation.
• Opening or removing covers that are marked with the triangular symbol with a lightning bolt may expose you to
electrical shock.
• Only a trained service technician should service components inside these compartments.
• If any of the following conditions occur, unplug the product from the electrical outlet and replace the part or contact your
trained service provider:
• The power cable, extension cable, or plug is damaged.
• An object has fallen into the product.
• The product has been exposed to water.
• The product has been dropped or damaged.
• The product does not operate correctly when you follow the operating instructions.
• Keep your system away from radiators and heat sources. Also, do not block cooling vents.
• Do not spill food or liquids on your system components, and never operate the product in a wet environment. If the system
gets wet, see the appropriate section in your troubleshooting guide or contact your trained service provider.
• Do not push any objects into the openings of your system. Doing so can cause fire or electric shock by shorting ou t interior
components.
• Use the product only with approved equipment.
• Allow the product to cool before removing covers or touching internal components.
• Operate the product only from the type of external power source indicated on the electrical ratings label. If you are not sure
of the type of power source required, consult your service provider or local power company.
• To help avoid damaging your system, be sure the voltage on the power supply is set to match the power available at your
location:
• 115 volts (V)/60 hertz (Hz) in most of North and South America and some Far Eastern countries such as South Korea
and Taiwan
• 100 V/50 Hz in eastern Japan and 100 V/60 Hz in western Japan
• 230 V/50 Hz in most of Europe, the Middle East, and the Far East
• –48 VDC for DC power supply unit on DES-3526DC only
• Also, be sure that attached devices are electrically rated to operate with the power available in your location.
• Use only approved power cable(s). If you have not been provided with a power cable for your system or for any AC-
powered option intended for your system, purchase a power cable that is ap proved for use in your country. The power cable
must be rated for the product and for the voltage and current marked on the product's electrical ratings label. The voltage and
current rating of the cable should be greater than the ratings marked on the product.
• To help prevent electric shock, plug the system and peripheral power cables into properly grounded electrical outlets. These
cables are equipped with three-prong plugs to help ensure proper grounding. Do not use adapter plugs or remove the
grounding prong from a cable. If you must use an extension cable, use a 3-wire cable with properly grounded plugs.
Page 13
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
xi
• Observe extension cable and power strip ratings. Make sur e that the total ampere rating of all products plugged into the
extension cable or power strip does not exceed 80 percent of the ampere ratings limit for the extension cable or power strip.
• To help protect your system from sudden, transient increases and decreases in electrical power, use a surge suppressor, line
conditioner, or uninterruptible power supply (UPS).
• Position system cables and power cables carefully; route cables so that they cannot be stepped on or tripped over. Be sure
that nothing rests on any cables.
• Do not modify power cables or plugs. Consult a licensed electrician or your power company for site modifications. Always
follow your local/national wiring rules.
• When connecting or disconnecting power to hot-pluggable power supplies, if offered with your system, observe the
following guidelines:
• Install the power supply before connecting the power cable to the power supply.
• Unplug the power cable before removing the power supply.
• If the system has multiple sources of power, disconnect power from the system by unplugging all power cables from
the power supplies.
• Move products with care; ensure that all casters and/or stabilizers are firmly connected to the system. Avoid sudden stops
and uneven surfaces.
General Precautions for Rack-Mountable Products
Observe the following precautions for rack stability an d safety. Also, refer to the rack installation documentation accompanying
the system and the rack for specific caution statements and procedures.
• Systems are considered to be components in a rack. Thus, "component" refers to any system as well as to various peripherals
or supporting hardware.
• Before working on the rack, make sure that the stabilizers are secured to the rack, extended to the floor, and that the full
weight of the rack rests on the floor. Install front and side stabilizers on a single rack or front stabilizers for joined multiple
racks before working on the rack.
• Always load the rack from the bottom up, and load the heaviest item in the rack first.
• Make sure that the rack is level and stable before extending a component from the rack.
• Use caution when pressing the component rail release latches and sliding a component into or out of a rack; the slide rails
can pinch your fingers.
• After a component is inserted into the rack, carefully extend the rail into a locking position, and then slide the component
into the rack.
• Do not overload the AC supply branch circuit that provides power to the rack. The total rack load should not exceed 80
percent of the branch circuit rating.
• Ensure that proper airflow is provided to components in the rack.
• Do not step on or stand on any component when servicing other components in a rack.
NOTE: A qualified electrician must perform all connections to DC power and to safety grounds.
All electrical wiring must comply with applicable local, regional or national codes and practices.
CAUTION: Never defeat the ground conductor or operate the equipment in the absence of a
suitably installed ground conductor. Contact the appropriate electrical inspection authority or an
electrician if you are uncertain that suitable grounding is available.
CAUTION: The system chassis must be positively grounded to the rack cabinet frame. Do not
attempt to connect power to the system until grounding cables are connected. A qualified
electrical inspector must inspect completed power and safety ground wiring. An energy hazard
will exist if the safety ground cable is omitted or disconnected.
Page 14
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
xii
Protecting Against Electrostatic Discharge
Static electricity can harm delicate components inside your system. To prevent static damage, discharge static electricity from
your body before you touch any of the electronic components, such as the microprocessor. You can do so by periodically touching
an unpainted metal surface on the chassis.
You can also take the following steps to prevent damage from electrostatic discharge (ESD):
1. When unpacking a static-sensitive component from its shipping carton, do not remove the component from the antistatic
packing material until you are ready to install the component in your system. Just before unwrapping the antistatic
packaging, be sure to discharge static electricity from your body.
2. When transporting a sensitive component, first place it in an antistatic container or packaging.
3. Handle all sensitive components in a static-safe area. If possible, use antistatic floor pads, workbench pads and an
antistatic grounding strap.
Page 15
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
1
Section 1
Introduction
Switch Description
Features
Ports
Front-Panel Components
Side Panel Description
Rear Panel Description
Gigabit Combo Ports
The DES-3500 layer 2 Fast Ethernet switches are members of the D-Link xStack
®
family. Ranging from 10/100Mbps edge
switches to core gigabit switches, the xStack
®
switch family has been future-proof designed to provide a stacking architecture with
fault tolerance, flexibility, port density, robust security and maximum throughput with a user-friendly management interface fo r
the networking professional.
The following manual describes the installation, maintenance and configurations concerning members of the xStack
®
DES-3500
switch series. These three switches, the DES-3526, DES-3526DC, and the DES-3550 are all very similar in configur ations and
basic hardware and consequentially, most of the information in this manual will be universal to the whole xStack
®
DES-3500
switch series. Corresponding screen pictures of the web manager may be taken from any one of these switches but the
configuration will be identical, except for varying port counts.
Switch Description
The DES-3500 Series switches are equipped with unshielded twisted-pair (UTP) cable ports providing dedicated 10 or 100 Mbps
bandwidth. The Switch has 24 UTP ports (48 UTP ports for the DES-3550) and Auto MDI-X /MDI-II co nver tible po r ts that can be
used for unlinking to another switch. These ports can be used for connecting PCs, printers, servers, hubs, routers, switches and
other networking devices. The dual speed ports use standard twisted-pair cabling and are ideal for segmenting networks into small,
connected sub networks for superior performance. Each 10/100 port can support up to 200 Mbps of throughp ut in full-duplex
mode.
In addition, the Switch has 2 Mini-GBIC combo ports. These two-gigabit combo ports are ideal for connecting to a server or
network backbone.
This stand-alone Switch enables the network to use some of the most demanding multimedia and imaging applications
concurrently with other user applications without creating bottlenecks. The built-in con sole interface can be used to configure the
Switch's settings for priority queuin g, VLANs, and port trunk groups, port monitoring, and port speed.
NOTE: For the remainder of this manual, all hardware versions of the DES-3500 Series
switches will be referred to as simply the Switch or the DES-3500 except where the differences
are relevant.
Features
• IEEE 802.3 10BASE-T compliant
• IEEE 802.3u 100BASE-TX compliant
• IEEE 802.1p Priority Queues
• IEEE 802.3x flow control in full duplex mode
• IEEE 802.3ad Link Aggregation Control Protocol
support.
• IEEE 802.1x Port-based and MAC-based Access
Control
• IEEE 802.1Q VLAN
• IEEE 802.1D Spanning Tree, IEEE 802.1W
Rapid Spanning Tree and IEEE 802.1s Multiple
Spanning Tree support
• Access Control List (ACL) support
• Single IP Management support
• Access Authentication Control utilizing
TACACS, XTACACS and TACACS+
• Dual Image Firmware
• Simple Network Time Protocol support
Page 16
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
2
• MAC Notification support
• Asymmetric VLAN support
• System and Port Utilization support
• System Log Support
• Address table: Supports up to 8K MAC addresses
per device
• Supports 16M Bytes buffer memory per device
• Supports Port-based VLAN Groups
• Port Trunking with flexible load distribution and
fail-over function
• IGMP Snooping support
• SNMP support
• Secure Sockets Layer (SSL) and Secure Shell
(SSH) support
• Port Mirroring support
• MIB support for:
• RFC1213 MIB II
• RFC1493 Bridge
• RFC1757 RMON
• RFC1643 Ether-like MIB
• RFC2233 Interface MIB
• Private MIB
• RFC2674 for 802.1p
• IEEE 802.1x MIB
• RS-232 DCE console port for Switch
management
• Provides parallel LED display for port status such
as link/act, speed, etc.
• High performance switching engine performs forwarding and filtering at full wire speed, maximum 14, 881 packets/sec
on each 10Mbps Ethernet port, and maximum 148,810 packet/sec on 100Mbps Fast Ethernet port.
• Full- and half-duplex for both 10Mbps and 100Mbps connections. Full duplex allows the switch port to simultaneously
transmit and receive data. It only works with connections to full-duplex-capable end stations and switches. Connections
to a hub must take place at half-duplex
• Support broadcast storm filtering
• Non-blocking store and forward switching scheme capability to support rate adaptation and protocol conversion
• Supports by-port Egress/Ingress rate control.
• Supports IP-MAC Port Binding.
• Efficient self-learning and address recognition mechanism enables forwarding rate at wire speed
• Safeguard Engine Support
Ports
• Twenty-four (48 for the DES-3550) high-performance (MDI -X/MDI-II) ports for connecting to end stations, servers,
hubs and other networking devices.
• All UTP ports can auto-negotiate between 10Mbps and 100Mbps, half-duplex and full duplex, and feature flow control.
• Two 1000BASE-T Mini-GBIC combo port s fo r c on necti n g t o anot he r s wi tc h, ser ver , or n et wo rk bac k bo ne.
• RS-232 DCE Diagnostic port (console port) for setting up and managing the Switch via a connection to a console
terminal or PC using a terminal emulation program.
NOTE: For customers interested in D-View, D-Link Corporation's proprietary SNMP
management software, go to the D-Link Website (www.dlink.com) and download the
software and manual.
Page 17
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
2
Front-Panel Components
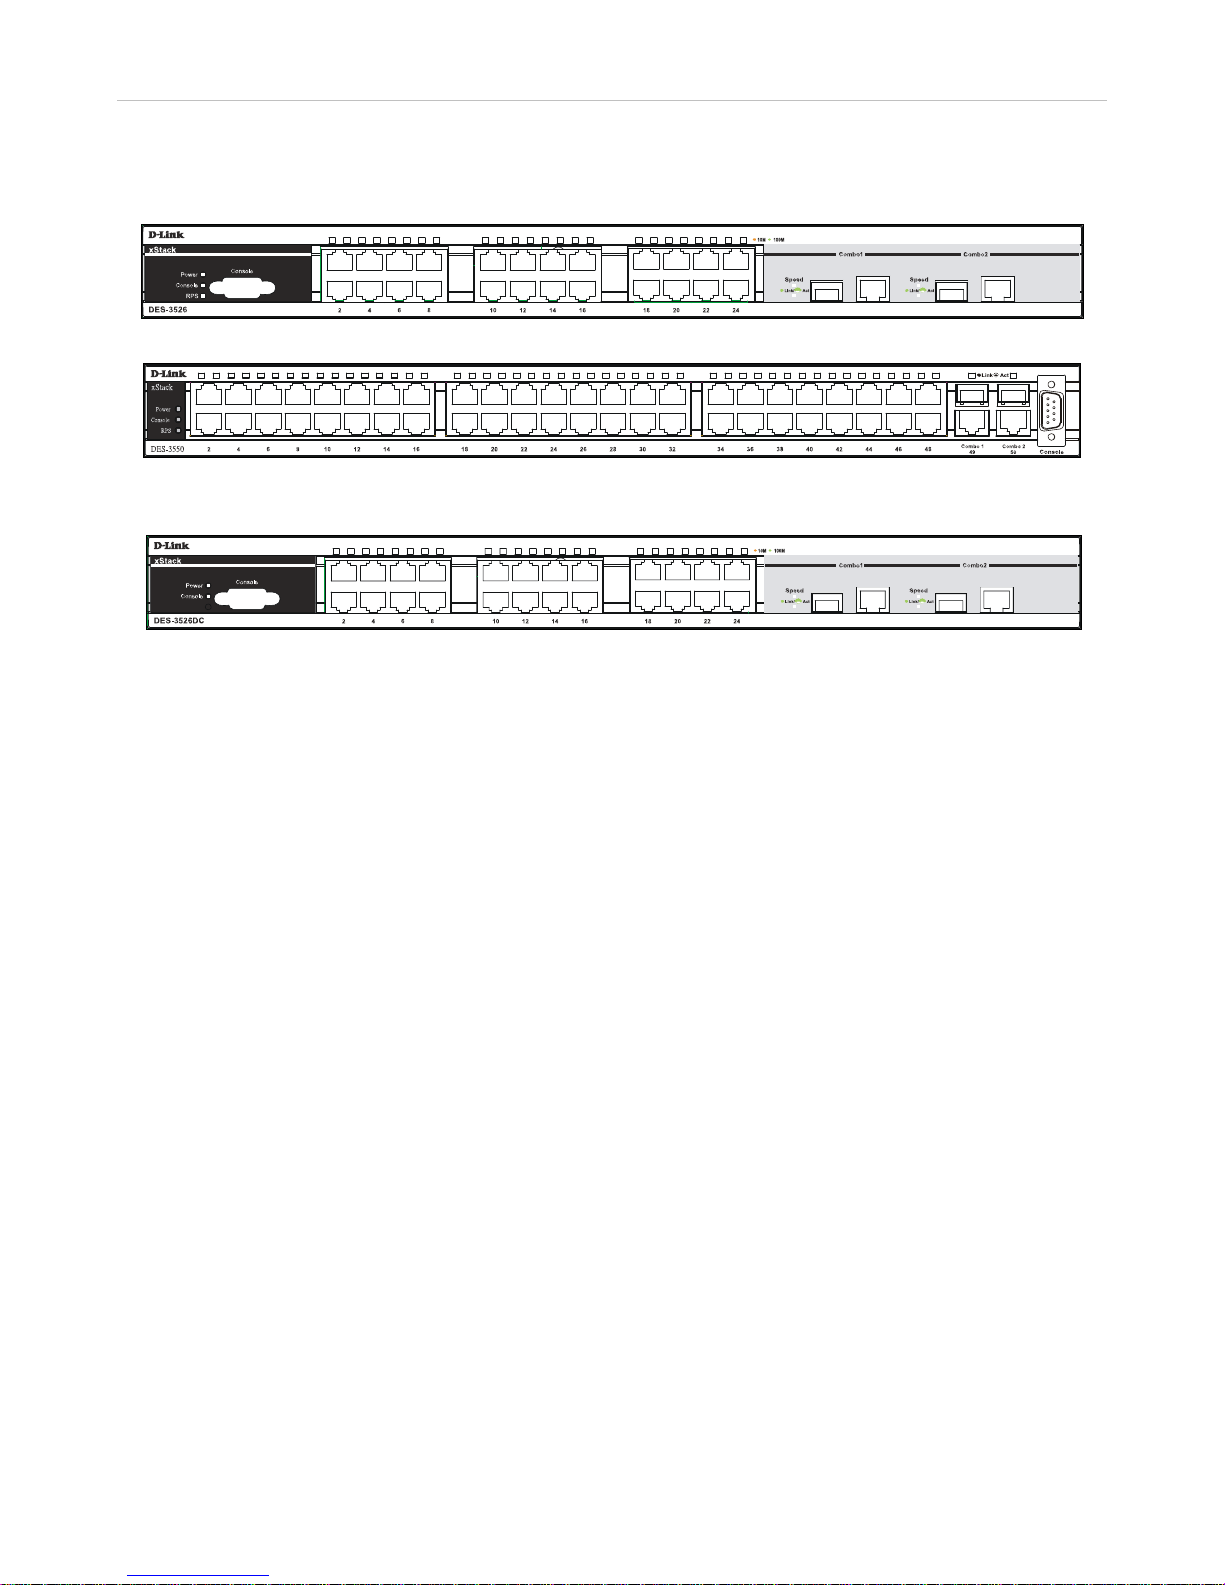
The front panel of the Switch consists of LED indicators for power and for each 10/100 Mbps twisted-pair ports, and two
1000BASE-T Mini-GBIC ports.
Figure 1- 1. Front Panel View of the DES-3526 switch
Figure 1- 2. Front Panel View of the DES-3550 switch
The DES-3526DC does not support a redundant power supply and theref ore the RPS indicator does not appear on the front panel.
Figure 1- 3. Front Panel View of DES-3526DC
Comprehensive LED indicators display the status of the Switch and the network.
Page 18
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
3
LED Indicators
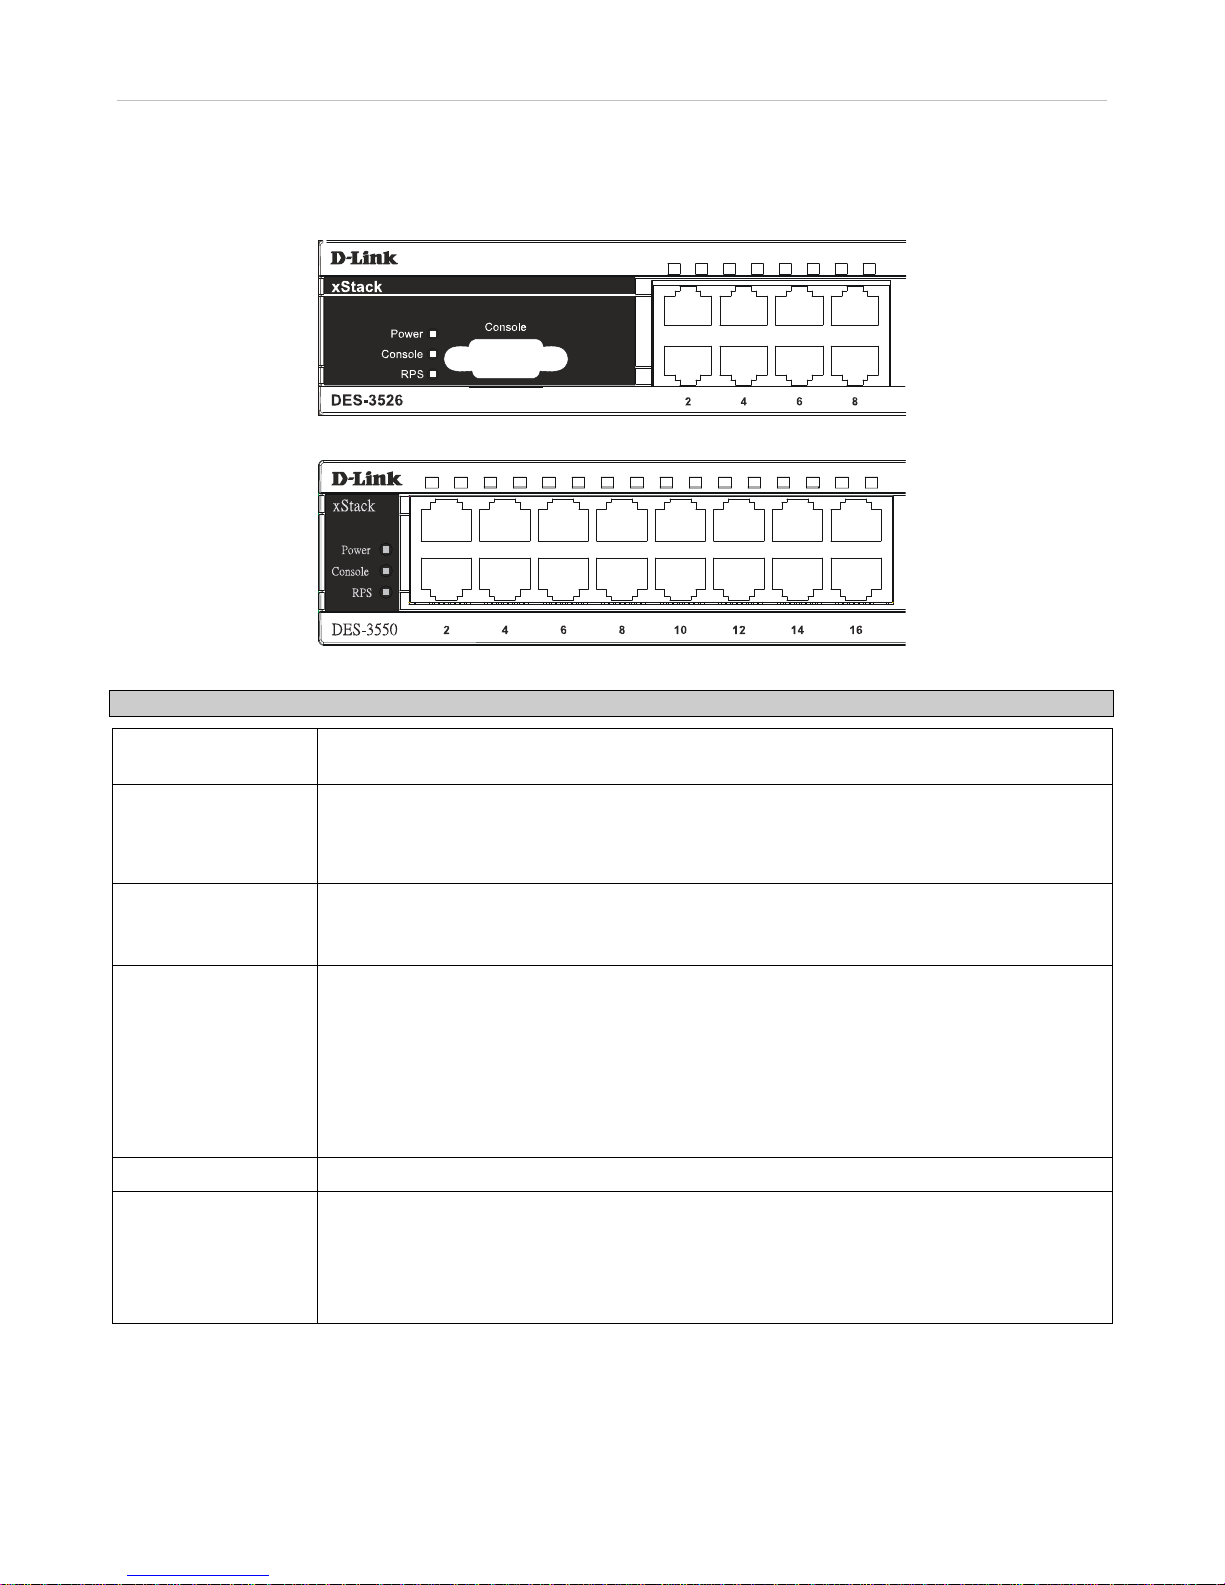
The Switch supports LED indicators for Power, Console, RPS (DES-3526/3550) and Port LEDs. The following shows the LED
indicators for the DES-3500 Series switches along with an explanation of each indicator. LEDs and there corresponding meanings
are displayed below.
Figure 1- 4. LED Indicators on DES-3526 Series switches
Figure 1- 5. Indicators on DES-3550 Series switch
LED Description
Power
This LED will light green after the Switch is powered on to indicate the ready state of the
device. The indicator is dark when the Switch is powered off.
Console
This LED should blink during the Power-On Self Test (POST). When the POST is finished,
the LED goes dark. This indicator is lit sold green when the Switch is being logged into via
out-of-band/local console management through the RS-232 console port in the back of the
Switch using a straight-through serial cable.
RPS
(DES-3526DC not
supported)
This LED will be lit when the redundant power supply is present and in use. Otherwise it will
remain dark.
Port LEDs
One row of LEDs for each port is located above the ports on the front panel. The first LED is
for the top port and the second one is for the bottom ports. These port LEDs will light two
different colors for 10M and 100M.
• Amber - For speeds of 10 Mbps. A solid light denotes activity on the port while a
blinking light indicates a valid link.
• Green - For speeds of 100 Mbps. A solid light denotes activity on the port while a
blinking light indicates a valid link.
100M/10M
These LEDs will light steady green to indicate that the port is transferring data at 100Mbps.
Gigabit Ports
The Switch's two Mini GBIC ports have their own corresponding LEDs:
Speed - This LED will light solid green when the port is transferring at a rate of 1000Mbps.
When dark, the port is transferring at 10/100Mbps.
Link/Act - This LED will light solid green when there is a valid link. A blinking LED indicates
current activity on the port. A dark LED indicates no activity on the port.
Page 19
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
4
Rear Panel Description
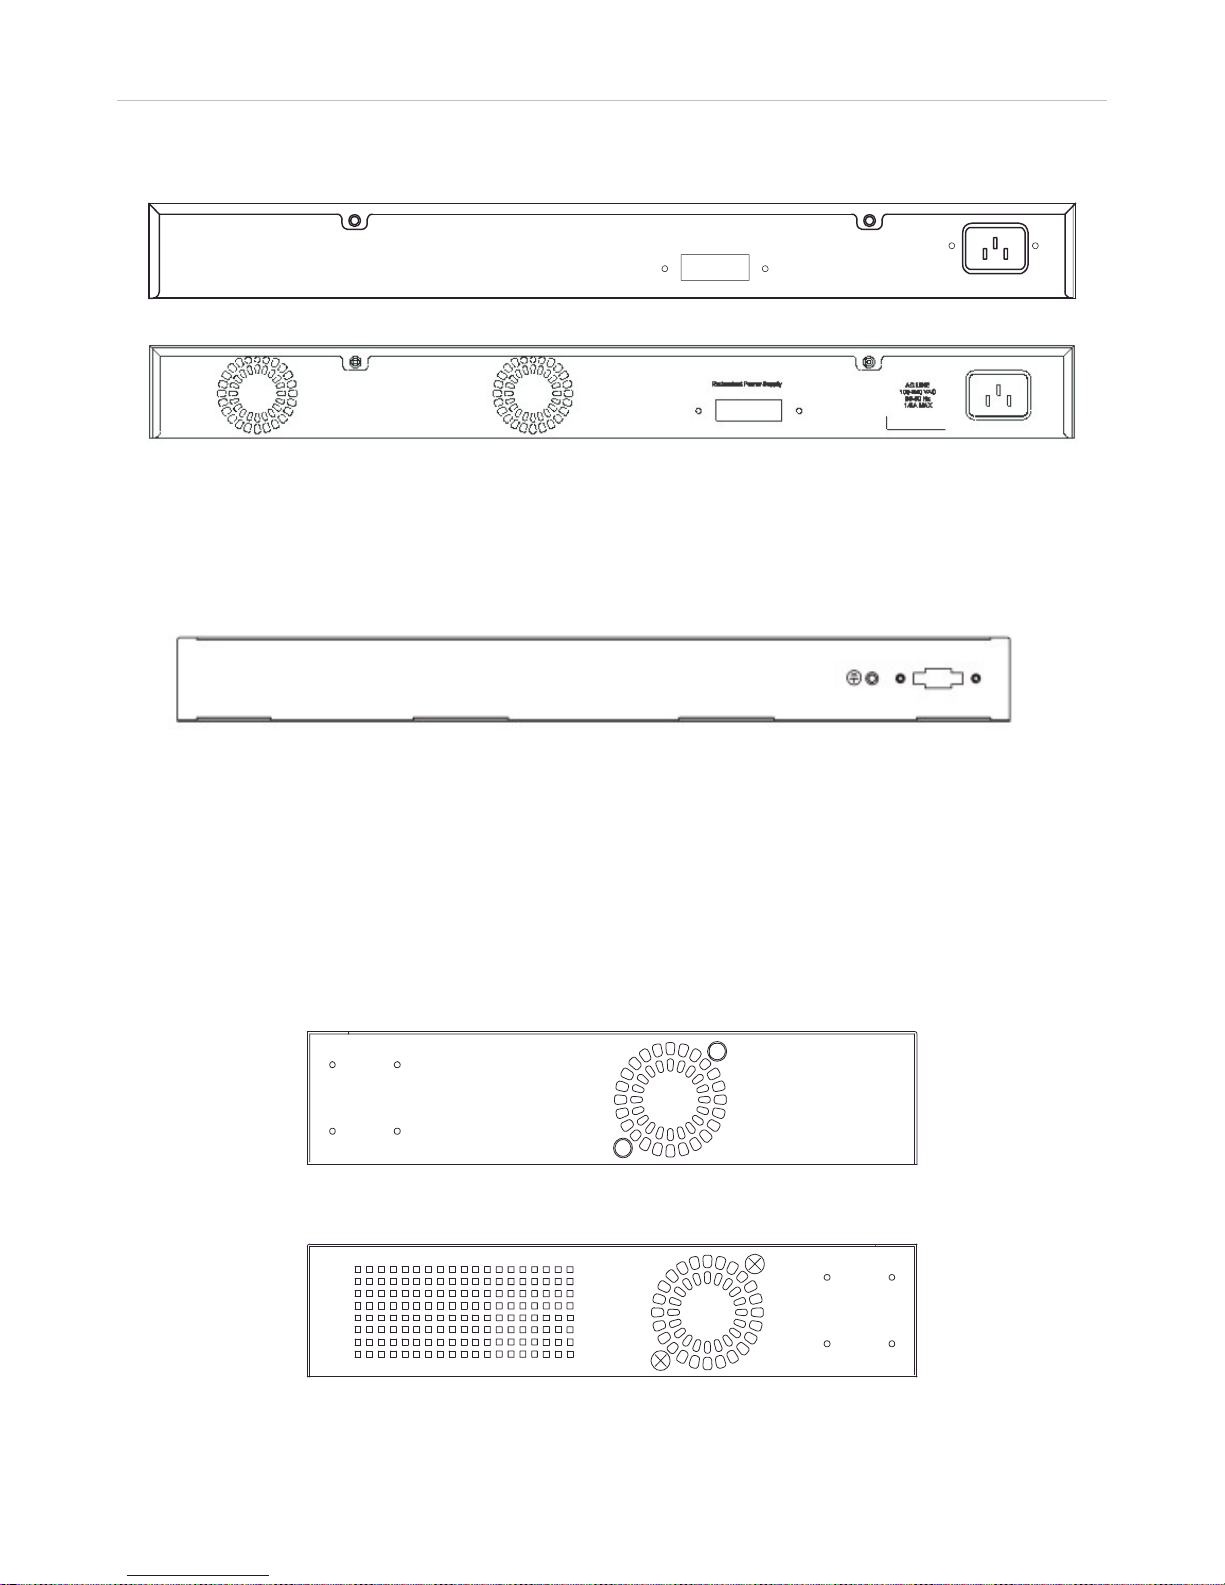
The rear panel of the Switch contains an AC power connector.
Figure 1- 6. Rear panel view of the DES-3526
Figure 1- 7. Rear panel view of the DES-3550
The AC power connector is a standard three-pronged connector that suppor ts the power cord. Plug-in the female connector of the
provided power cord into this socket, and the male side of the cord into a power ou tlet. The Switch automatically adju sts its power
setting to any supply voltage in the range from 100 ~ 240 VAC at 50 ~ 60 Hz.
The rear panel also includes an outlet for an optional external power supply. When power fails, the optional external RPS will take
over all the power immediately and automatically.
Figure 1- 8. Rear panel view of DES-3526DC
The rear panel of the DC power version of the Switch includes an opening designed to accommodate the DC power wiring
assembly. See the installation instructions in this Section for details.
Side Panel Description
The right-hand side panel of the Switch contains a system fan, while the left hand panel includes a system fan and a heat vent.
The system fans are used to dissipate heat. The sides of the system also provide heat vents to serve the same purpose. Do not
block these openings, and leave at least 6 inches of space at the rear and sides of the Switch for proper ventilation. Be reminded
that without proper heat dissipation and air circulation, system components might overheat, which could lead to system failure.
Figure 1- 9. Side panels of the DES-3526/DES-3526DC
Page 20
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
5
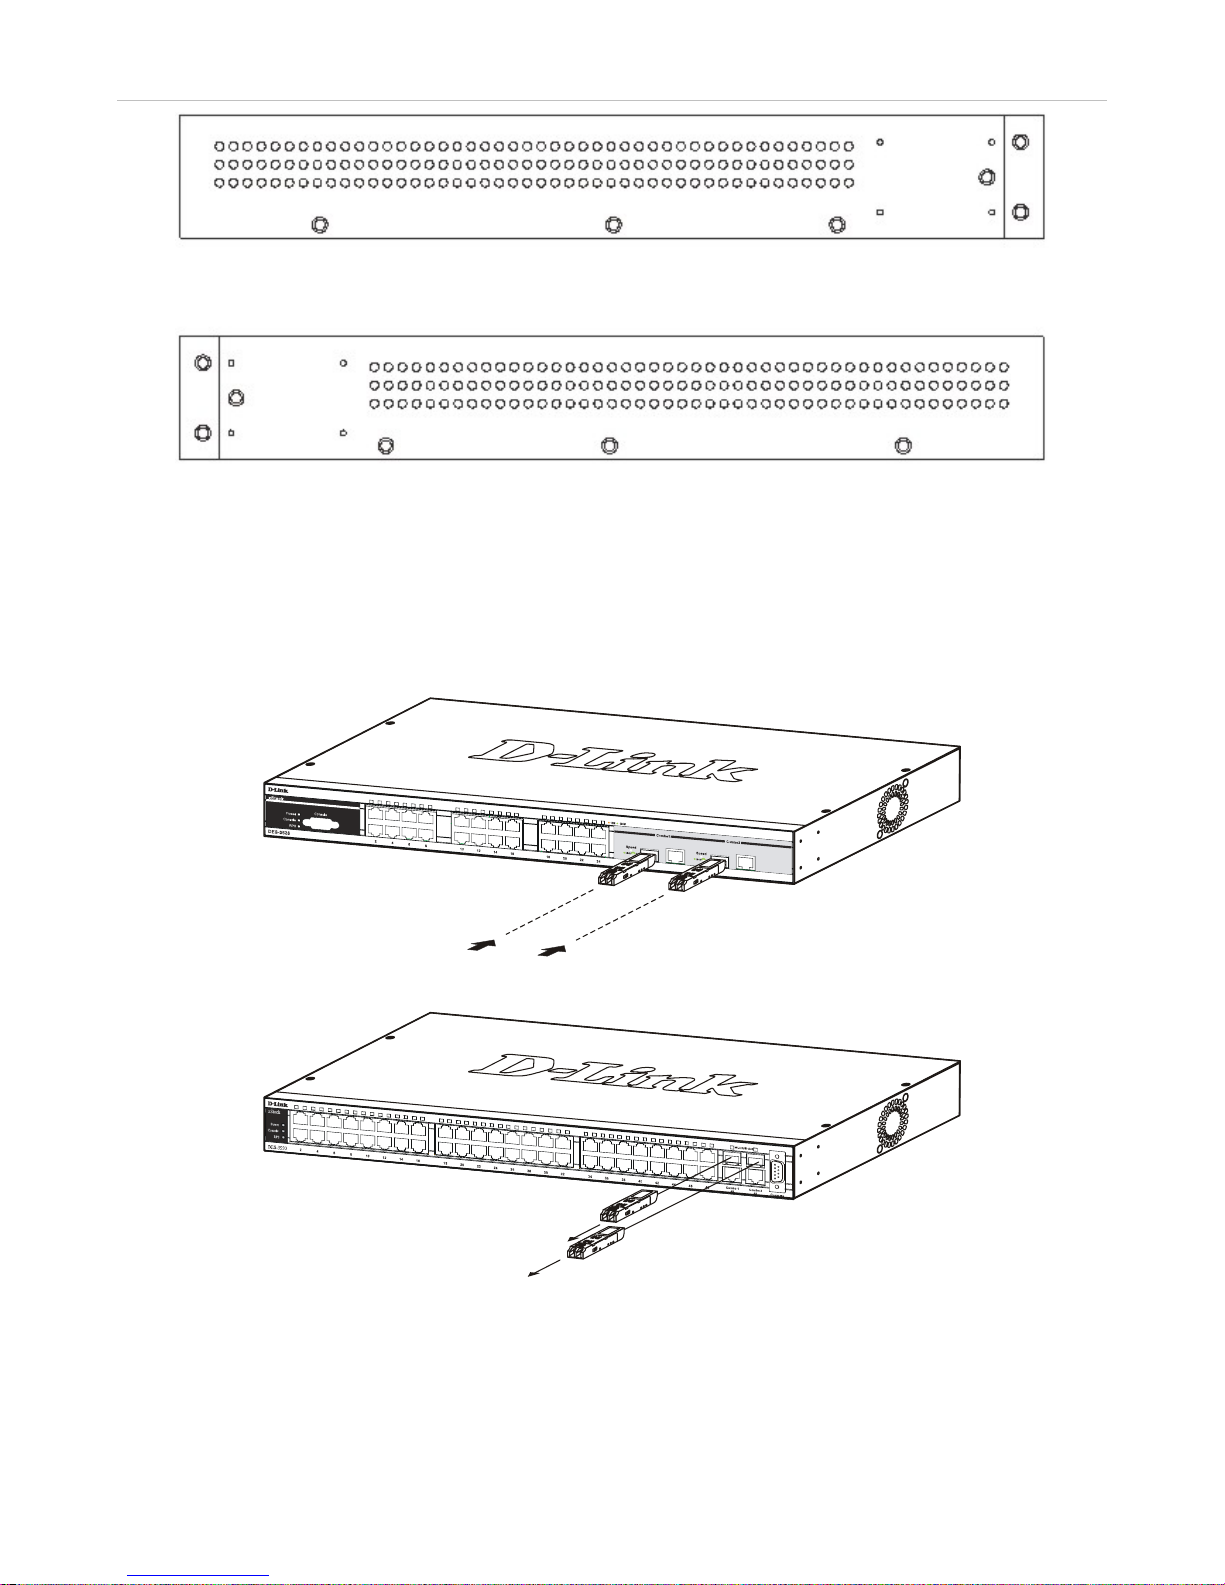
Figure 1- 10. Side panels of the DES-3550
Gigabit Combo Ports
In addition to the 24 (or 48) 10/100 Mbps ports, the Switch features two Gigabit Ethernet Co mbo ports. These two ports are
1000BASE-T copper ports (provided) and Mini-GBIC ports (optional). See the diagram below to view the two Mini-GBIC port
modules being plugged into the Switch. Please note that although these two front panel modules can be used simultaneously, the
ports must be different. The GBIC port will always have the highest priority.
Figure 1- 11. Inserting the Mini-GBIC modules into the DES-3526
Figure 1- 12. Inserting the Mini-GBIC modules into the DES-3550
Page 21

xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
6
Figure 1- 13. Installing the Mini-GBIC Module
Page 22
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
7
SECTION 2
Installation
Package Contents
Before You Connect to the Network
Installing the Switch without the Rack
Rack Installation
Power On
Package Contents
Open the shipping carton of the Switch and carefully unpack its contents. The carton should contain the following items:
• One xStack
®
DES-3500 Series switch
• One AC power cord
• One CD Kit for User’s Guide/CLI/D-View module
• Quick Installation Guide
• Registration card
• Mounting kit (two brackets and screws)
• Four rubber feet with adhesive backing
• RS-232 console cable
If any item is found missing or damaged, please contact your local D-Link Reseller for replacement.
Before You Connect to the Network
The site where you install the Switch may greatly affect its performance. Please follow these guidelines for setting up the Switch.
• Install the Switch on a sturdy, level surface that can support at least 6.6 lb. (3 kg) of weight. Do not place heavy objects
on the Switch.
• The power outlet should be within 1.82 m et e rs (6 feet) of the Swit ch .
• Visually inspect the power cord and see that it is fully secured to the AC power port.
• Make sure that there is proper heat dissipation from and adequate ventilation around the Switch. Leave at least 10 cm (4
inches) of space at the front and rear of the Switch for ventilation.
• Install the Switch in a fairly cool and dry place for the acceptable temperature and humidity operating ranges.
• Install the Switch in a site free from strong electromagnetic field generators (such as motors), vibration, dust, and direct
exposure to sunlight.
• When installing the Switch on a level surface, attach the rubber feet to the bottom of the device. The rubber feet
cushion the Switch, protect the casing from scratches and prevent it from scratching other surfaces.
Page 23
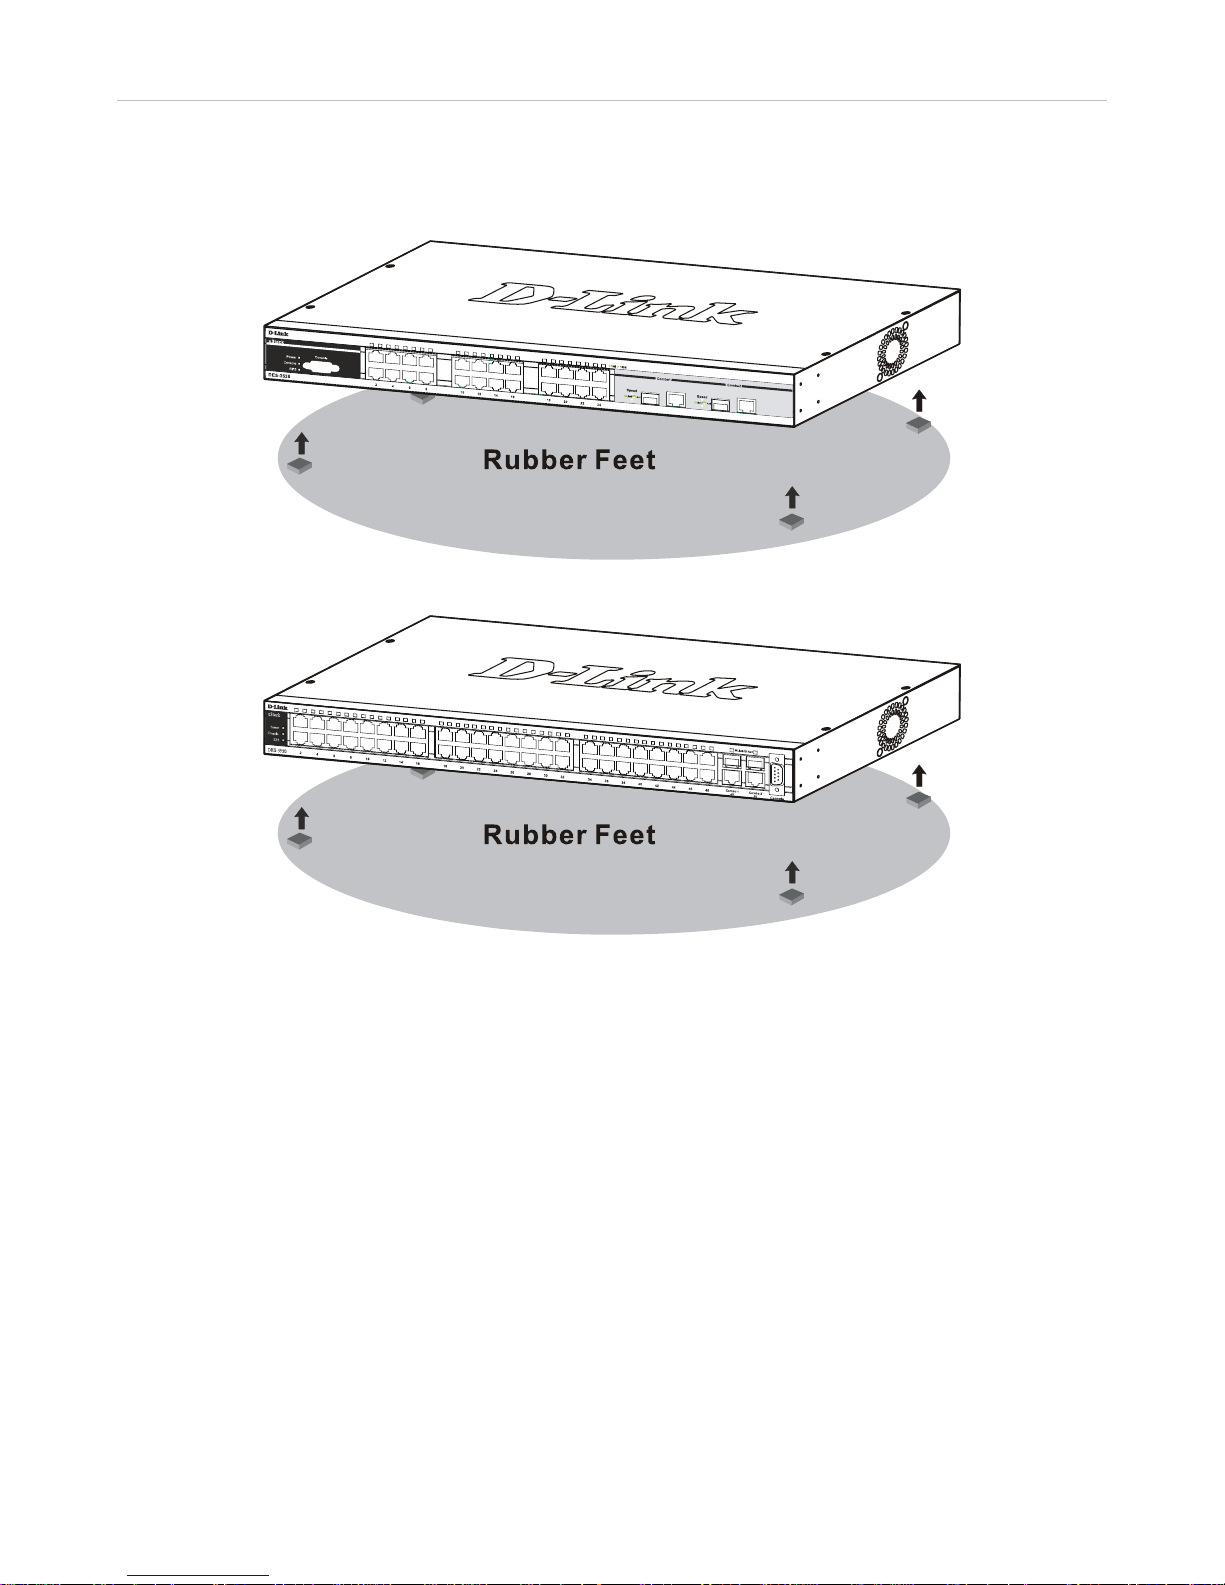
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
8
Installing the Switch without the Rack
When installing the Switch on a desktop or shelf, the rubber feet included with the Switch should first be attached. Attach these
cushioning feet on the bottom at each corner of the device. Allow enough ventilation space between the Switch and any other
objects in the vicinity.
Figure 2- 1. Preparing the DES-3526 for installation on a desktop or shelf
Figure 2- 2. Preparing the DES-3550 for installation on a desktop or shelf
Page 24
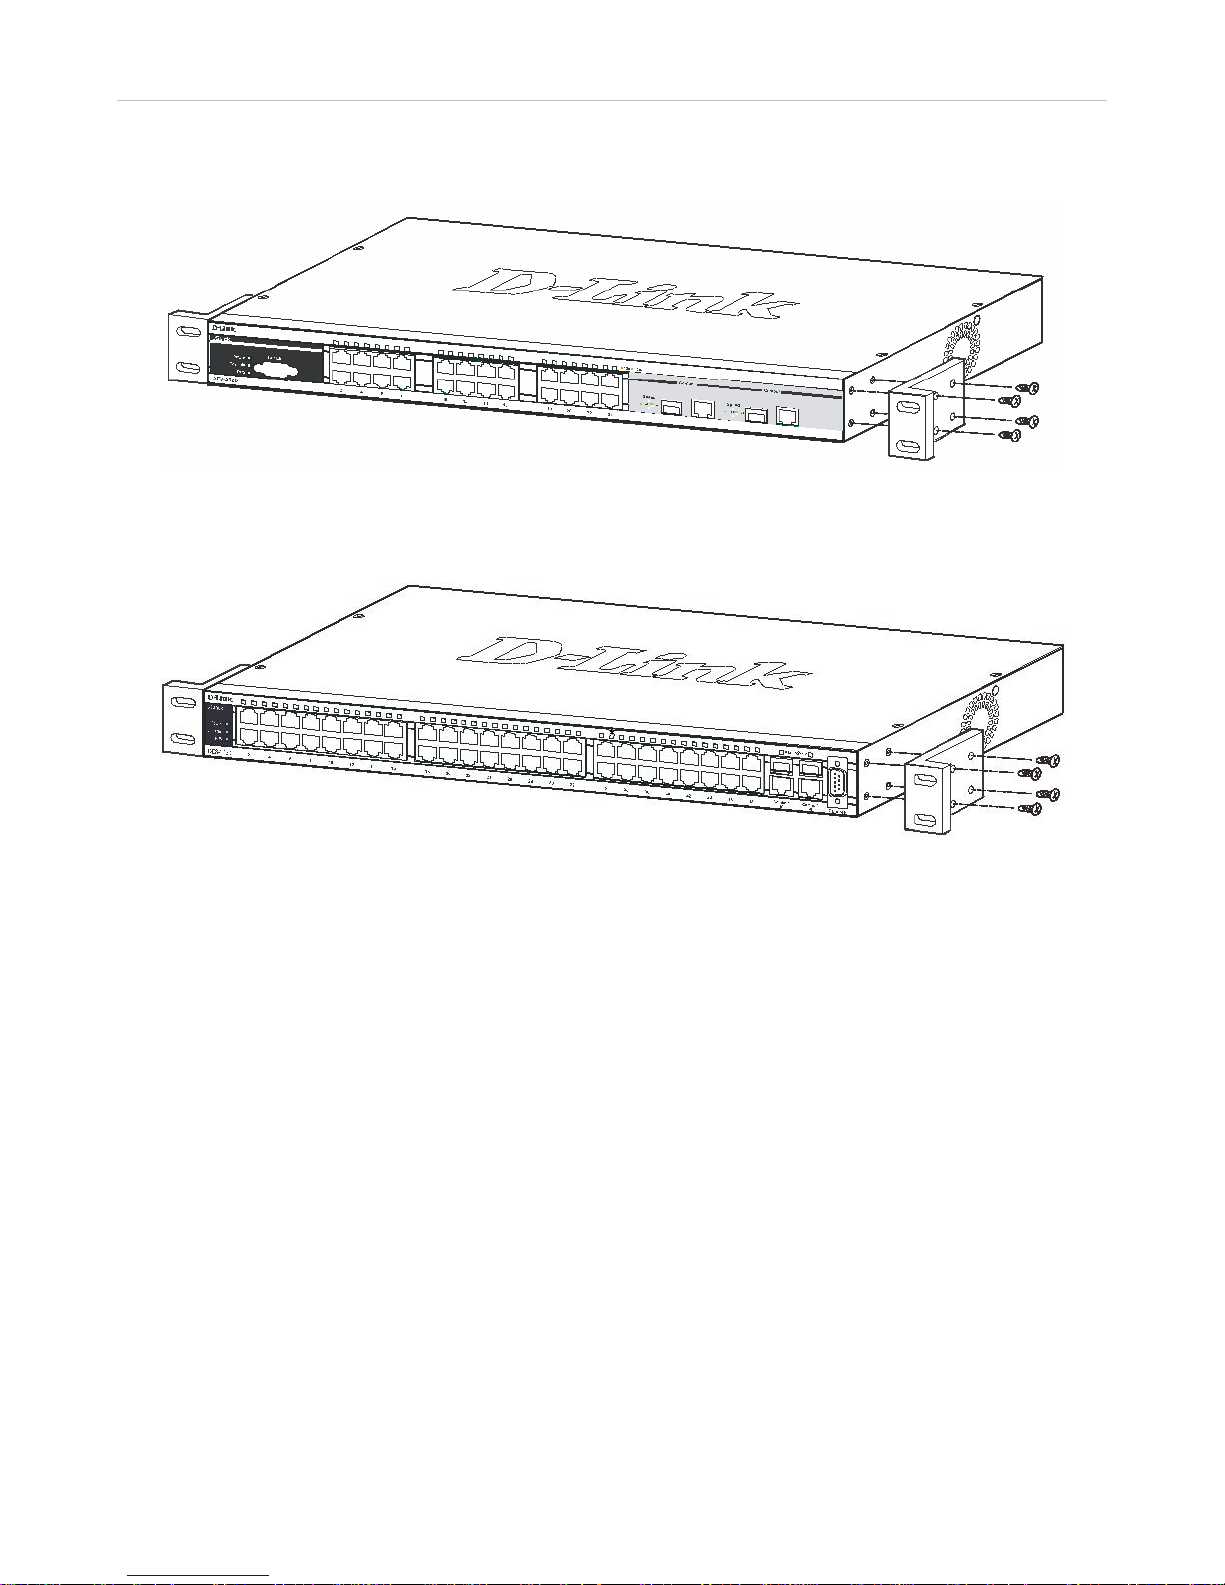
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
9
Installing the Switch in a Rack
The Switch can be mounted in a standard 19" rack. Use the following diagrams to guide you.
Figure 2- 3. Fasten mounting brackets to the DES-3526
Figure 2- 4. Fasten mounting brackets to the DES-3550
Fasten the mounting brackets to the Switch using the screws provided. W ith the brackets attached securely, you can mount the
Switch in a standard rack as shown in Figure 2-3 below.
Page 25
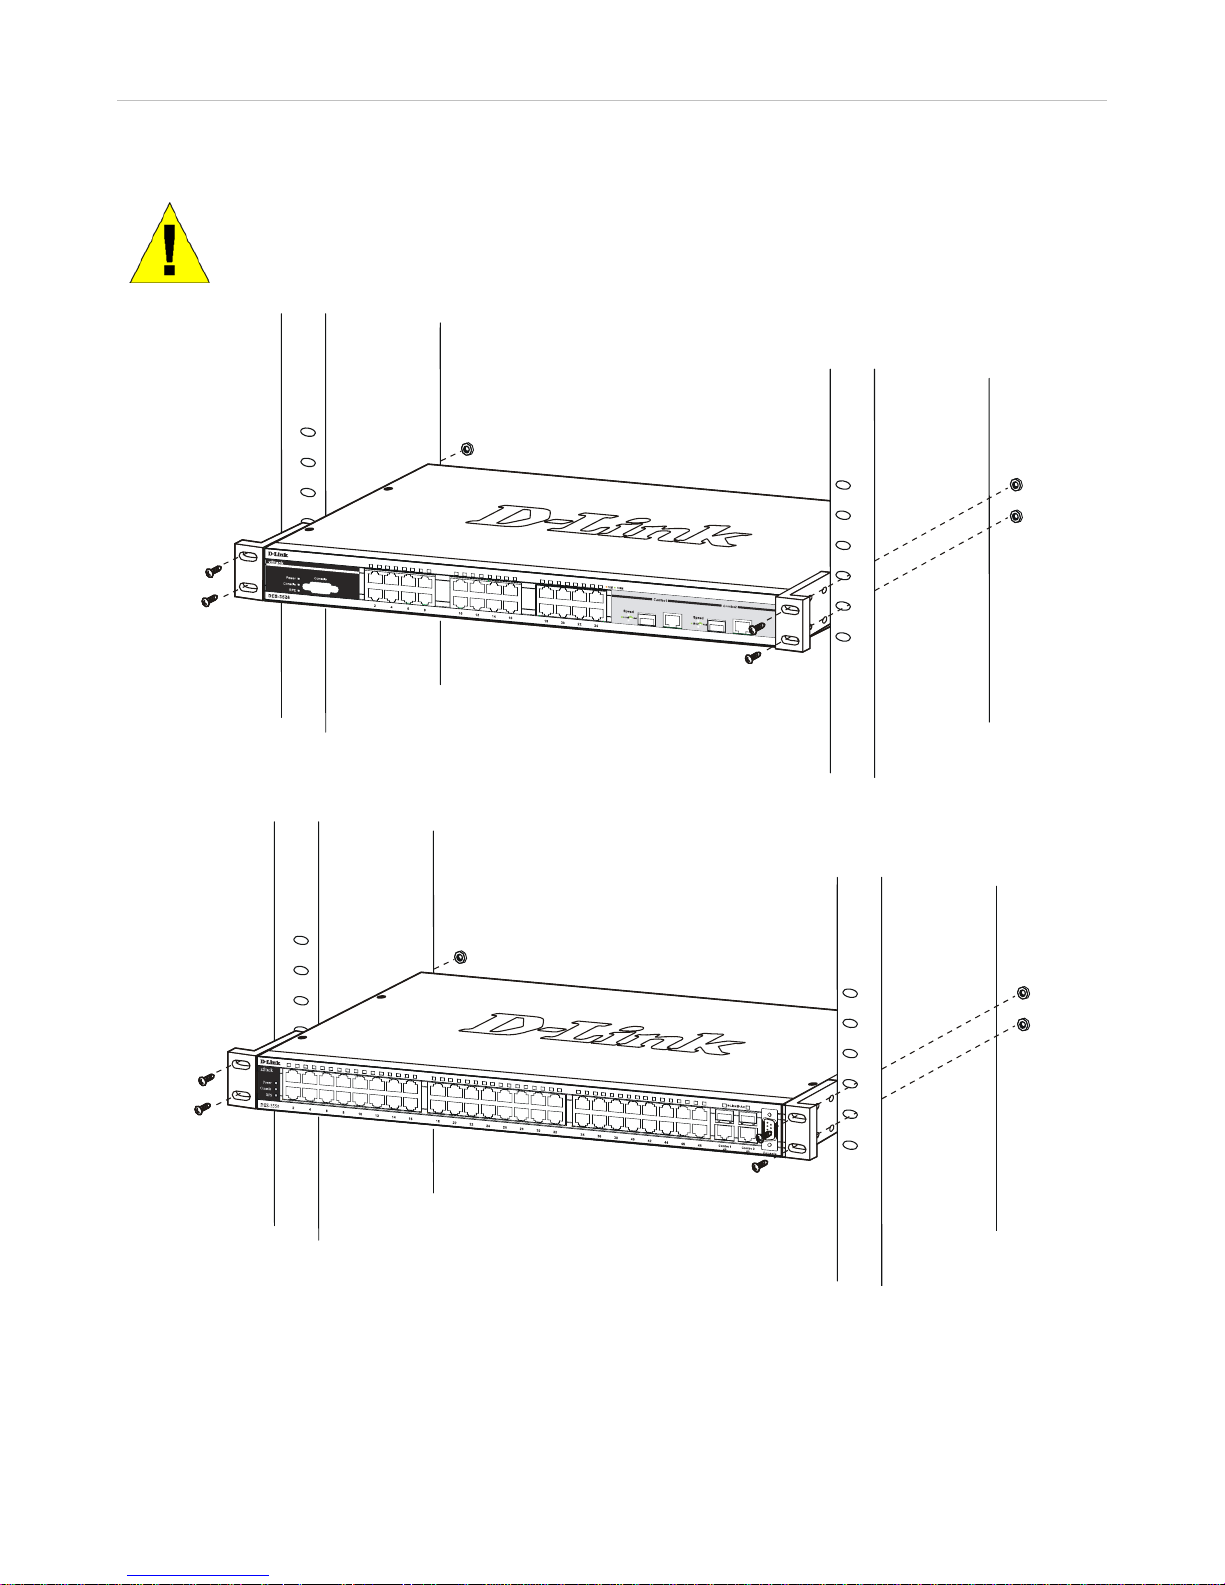
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
10
Mounting the Switch in a Standard 19" Rack
CAUTION: Installing systems in a rack without the front and side stabilizers installed could cause the
rack to tip over, potentially resulting in bodily injury under certain circumstances. Therefore, always
install the stabilizers before installing components in the rack. After installing components in a rack, do
not pull more than one component out of the rack on its slide assemblies at one time. The weight of
more than one extended component could cause the rack to tip over and may result in injury.
Figure 2- 5. Installing the DES-3526 in a rack
Figure 2- 6. Installing the DES-3550 in a rack
Page 26
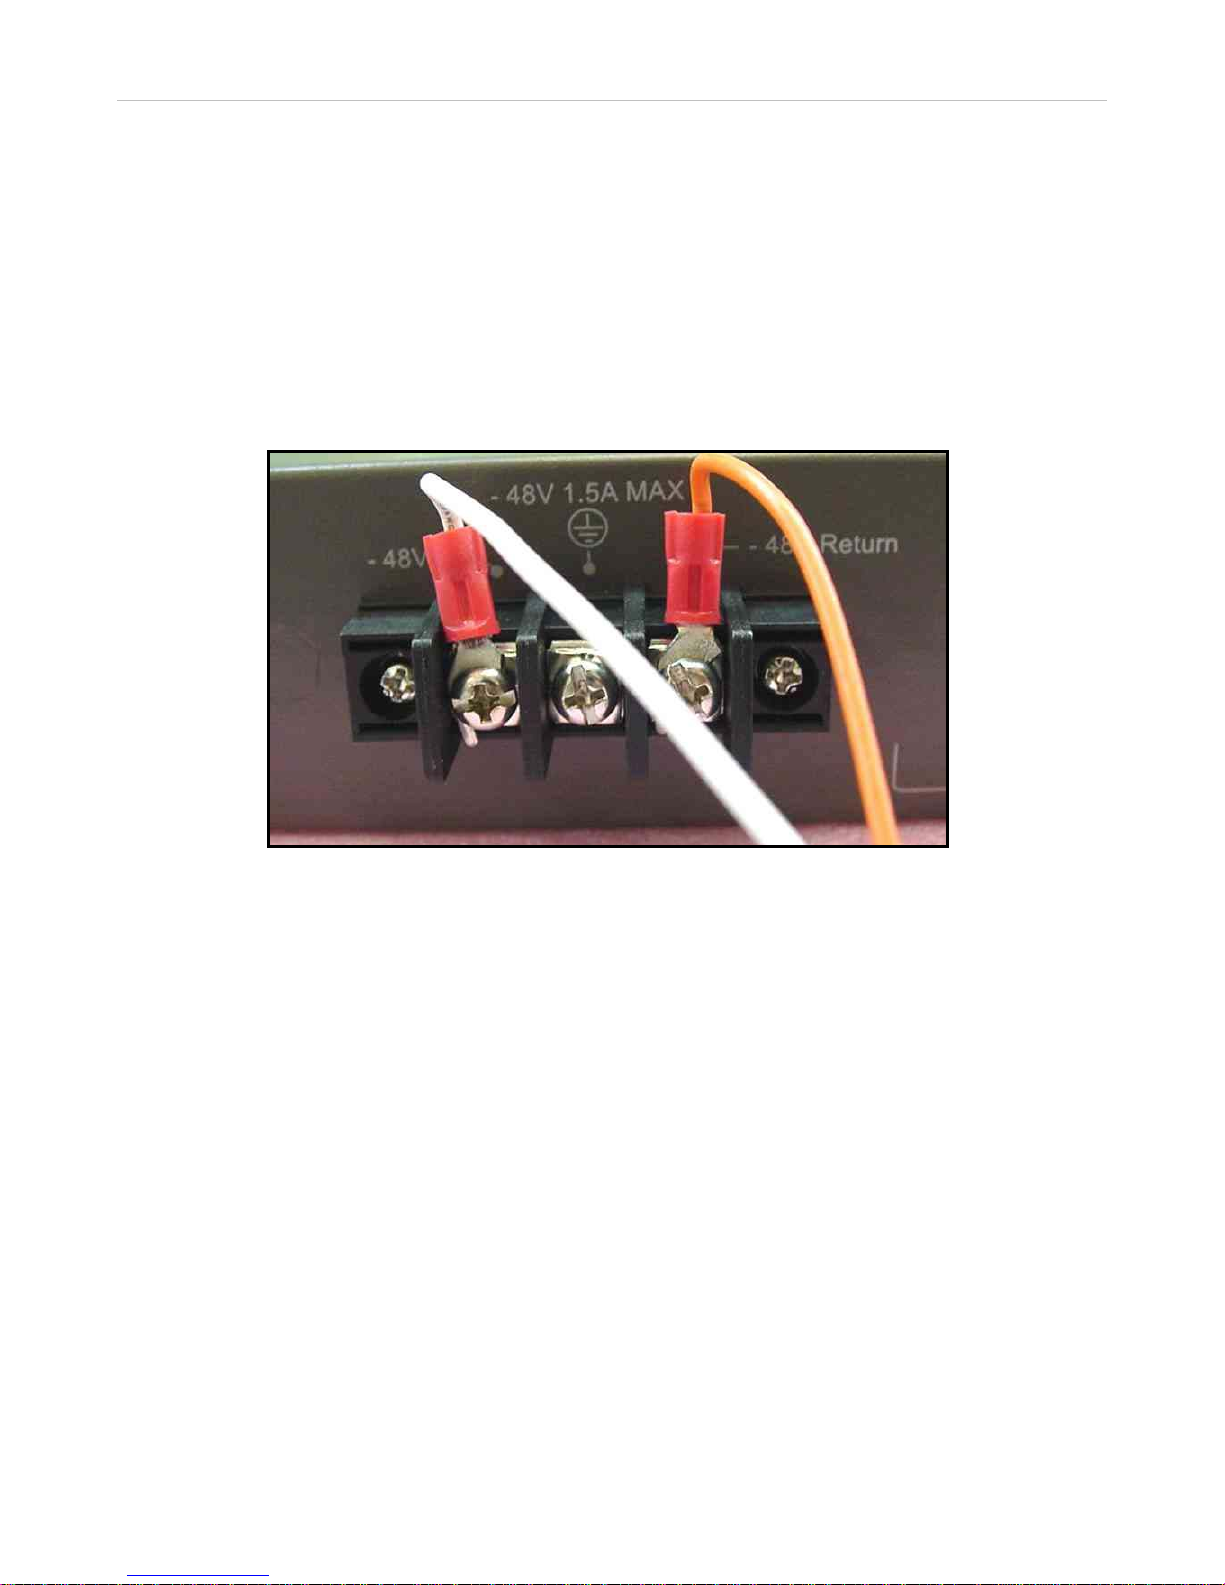
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
11
Power On (AC Power)
Plug one end of the AC power cord into the power connector of the Switch and the other end into the local power source outlet.
After the Switch is powered on, the LED indicators will momentarily blink. This blinking of the LED indicators represents a reset
of the system.
Power Failure
As a precaution for AC power supply units, in the event of a power failure, unplug the Switch. When power has resumed, plug the
Switch back in.
Connecting DC Power to DES-3526DC
Follow the instructions below to connect the DC power supply of the DES-352 6DC to a DC power source.
Figure 2- 7. Power connections attached to contacts on assembly
1. Firmly attach the DC power to the negative and positive contacts on the wiring assembly.
• The negative pole (-) connects to the -48V contact.
• The positive pole (+) connects to the -48V Return contact.
• If available, the earth ground may be connected to center contact post.
2. Tighten the contact screws so the connection is secure.
Page 27
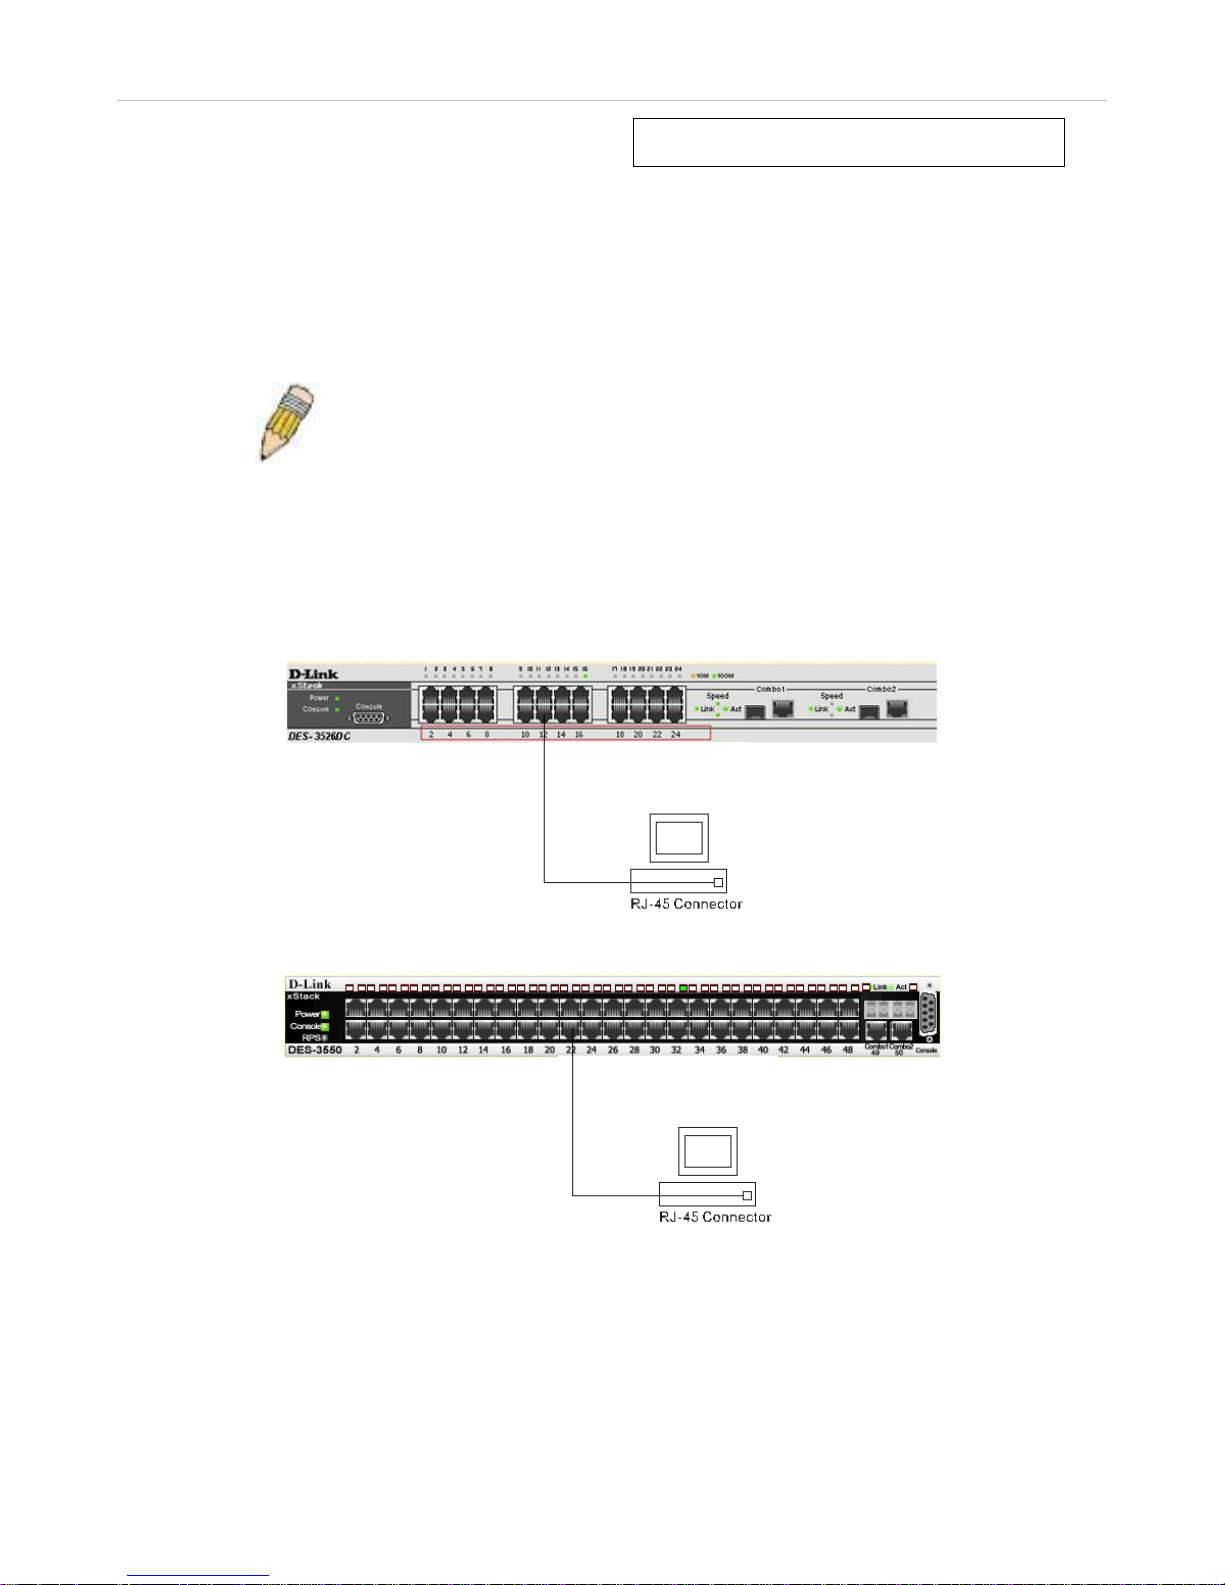
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
12
Section 3
Connecting the Switch
Switch to End Node
Switch to Hub or Switch
Connecting To Network Backbone or Server
NOTE: All 24 (48 for the DES-3550) high-performance NWay Ethernet
ports can support both MDI-II and MDI-X connections.
Switch to End Node
End nodes include PCs outfitted with a 10, 100 or 1000 Mbps RJ-45 Ethernet/Fast Ethernet Network Interface Card (NIC) and
most routers.
An end node can be connected to the Switch via a twisted-pair Category 3, 4, or 5 UTP/STP cable. The end node should be
connected to any of the ports of the Switch.
Figure 3- 1. DES-3526 connected to an end node
Figure 3- 2 DES-3550 connected to an end node
The Link/Act LEDs for each UTP port will light green or amber when the link is valid. A blinking LED indicates packet activity
on that port.
Page 28

xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
13
Switch to Hub or Switch
These connections can be accomplished in a number of ways using a normal cable.
• A 10BASE-T hub or switch can be connected to the Switch via a twisted-pair Category 3, 4 or 5 UTP/STP cable.
• A 100BASE-TX hub or switch can be connected to the Switch via a twisted -pair Category 5 UTP/STP cable.
Figure 3- 3. DES-3526 connected to a normal (non-Uplink) port on a hub or switch using a straight or
crossover cable
Figure 3- 4 DES-3550 connected to a normal (non-Uplink) port on a hub or switch using a straight or
crossover cable
Page 29
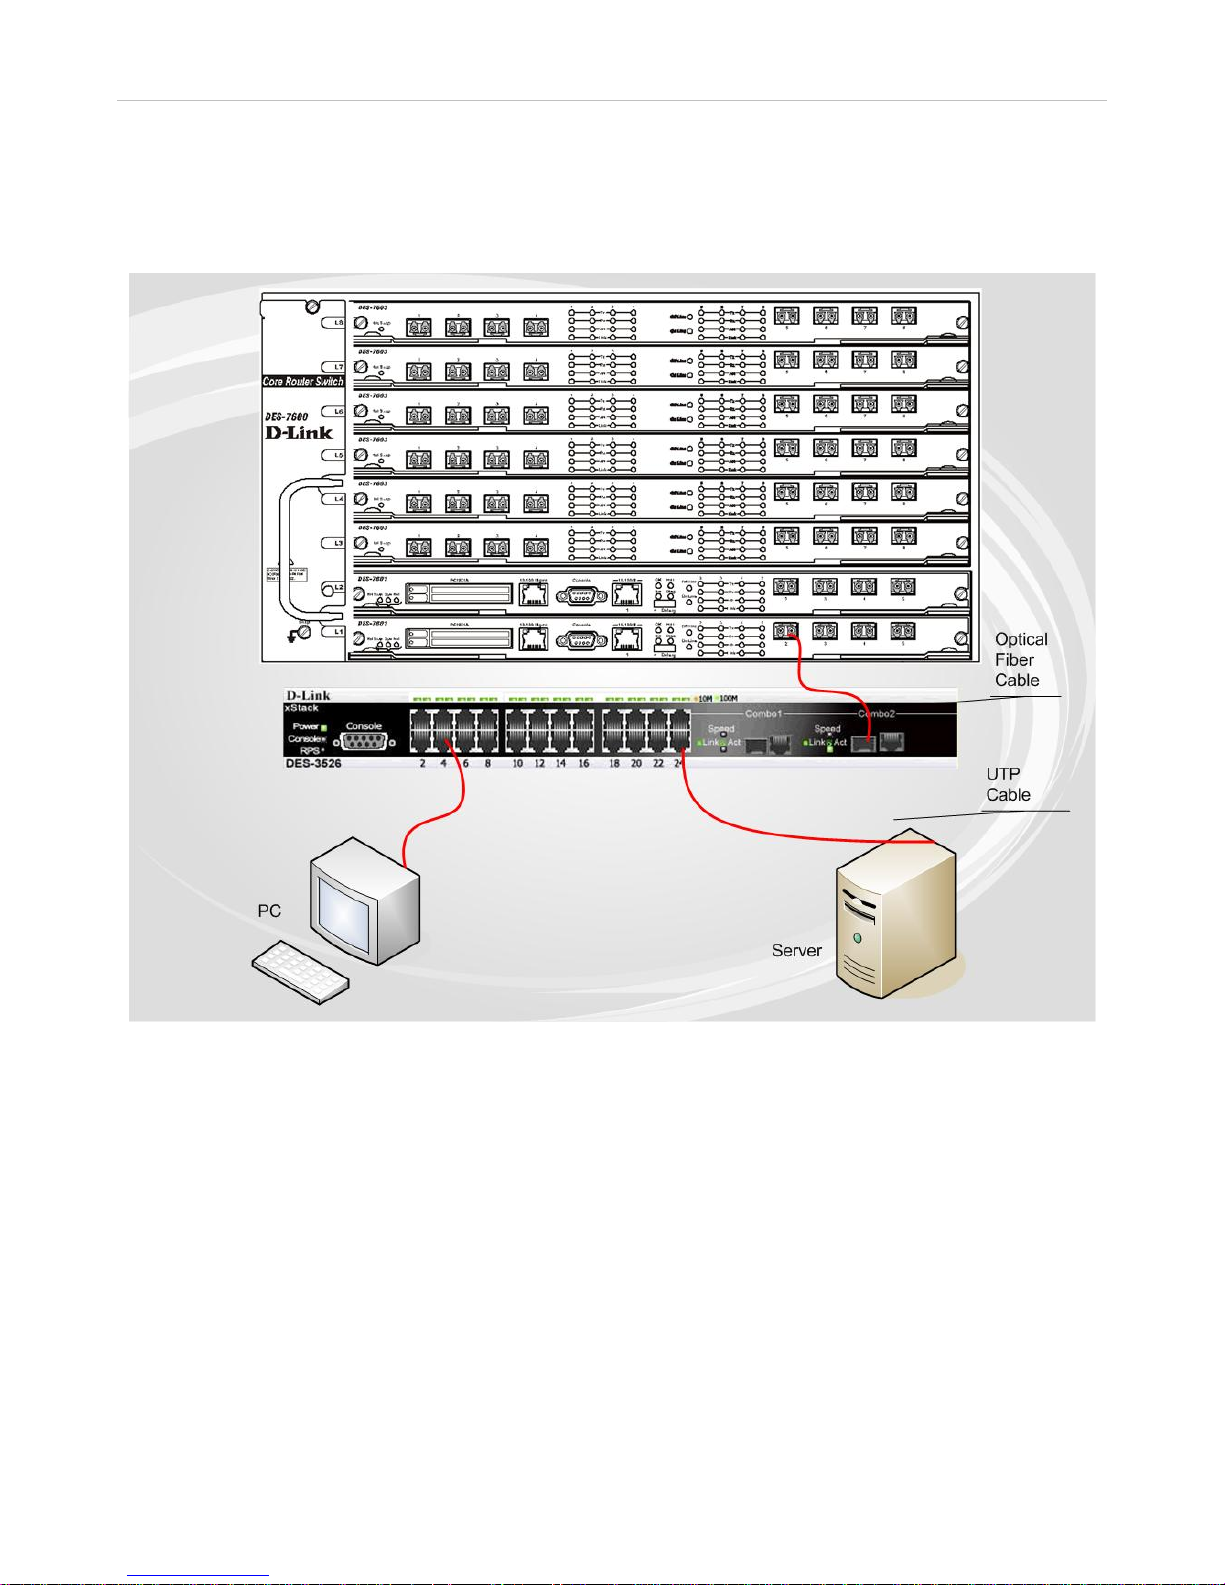
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
14
Connecting To Network Backbone or Server
The two Mini-GBIC combo ports are ideal for unlinking to a network backbone or server. The copper ports operate at a speed of
1000, 100 or 10Mbps in full or half duplex mode. The fiber optic ports can operate at 1000Mbps in full duplex mode.
Connections to the Gigabit Ethernet ports are made using fiber optic cable or Category 5 copper cable, depending on the type of
port. A valid connection is indicated when the Link LED is lit.
Figure 3- 5. Connecting the DES-3500 Series switch to a Server
Page 30
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
15
Section 4
Introduction to Switch Management
Management Options
Web-based Management Interface
SNMP-Based Management
Managing User Accounts
Command Line Console Interface through the Serial Port
Connecting the Console Port (RS-232 DCE)
First Time Connecting to the Switch
Password Protection
SNMP Settings
IP Address Assignment
Connecting Devices to the Switch
Management Options
This system may be managed out-of-band through the console port on the front panel or in-band using Telnet. The user may also
choose the web-based management, accessible through a web browser.
Web-based Management Interface
After you have successfully installed the Switch, you can configure the Switch, monitor the LED panel, and display statistics
graphically using a web browser, such as Netscape Navigator (version 6.2 and higher) or Microsoft® Internet Explorer (version
5.0).
SNMP-Based Management
You can manage the Switch with an SNMP-compatible console program. The Switch supports SNMP version 1.0, version 2.0 and
version 3.0. The SNMP agent decodes the incoming SNMP messages and responds to requests with MIB objects stored in the
database. The SNMP agent updates the MIB objects to generate statistics and counters.
Connecting the Console Port (RS-232 DCE)
The Switch provides an RS-232 serial port that enables a connection to a computer or terminal for monitoring and configuring the
Switch. This port is a female DB-9 connector, implemented as a data terminal equipment (DTE) connection.
To use the console port, you need the following equipment:
• A terminal or a computer with both a serial port and the ability to emulate a terminal.
• A null modem or crossover RS-232 cable with a female DB-9 connector for the console port on the Switch.
Page 31
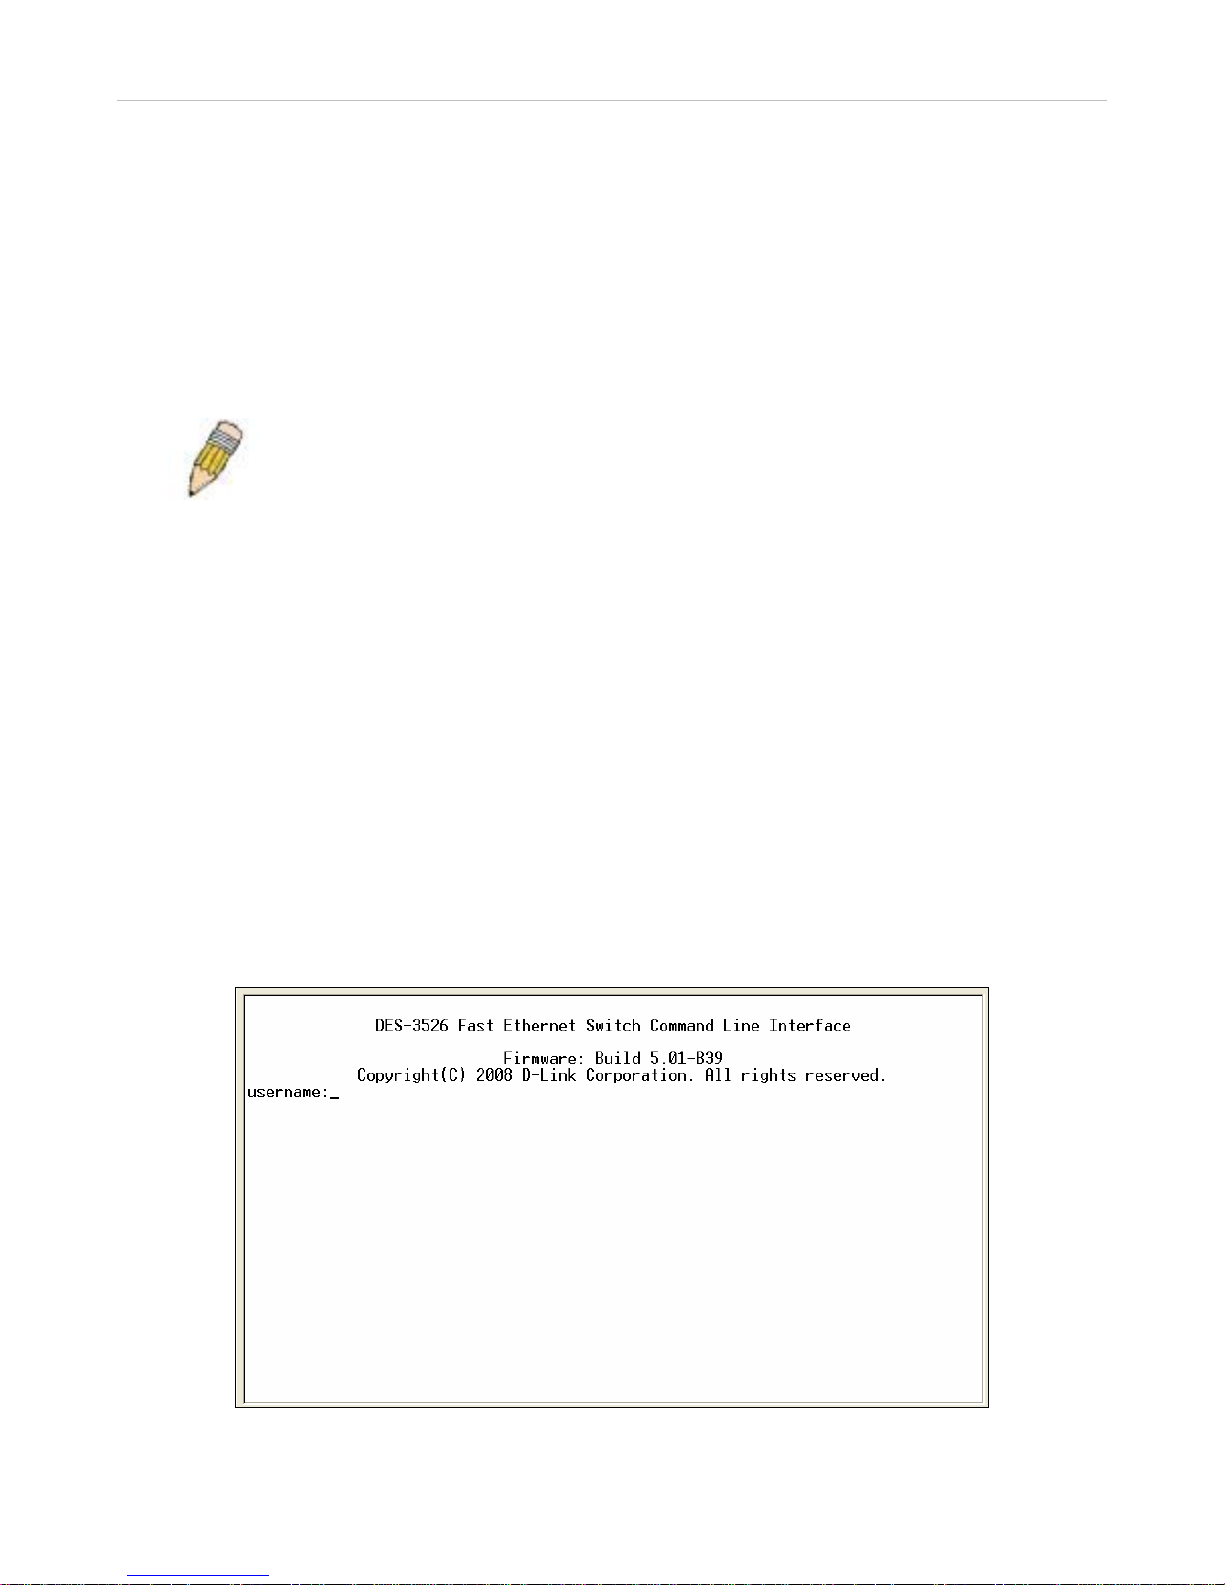
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
16
To connect a terminal to the console port:
1. Connect the female connector of the RS-232 cable directly to the console port on the Switch, and tighten the captive
retaining screws.
2. Connect the other end of the cable to a terminal or to the serial connector of a computer running terminal emulation
software. Set the terminal emulation software as follows:
3. Select the appropriate serial port (COM port 1 or COM port 2).
4. Set the data rate to 9600 baud.
5. Set the data format to 8 data bits, 1 stop bit, and no parity.
6. Set flow control to none.
7. Under Properties, select VT100 for Emulation mode.
8. Select Terminal keys for Function, Arrow, and Ctrl keys. Ensure that you select Terminal keys (not Windows keys).
9. After you have correctly set up the terminal, plug the power cable into the power receptacle on the back of the Switch.
The boot sequence appears in the terminal.
10. After the boot sequence completes, the console login screen displays.
11. If you have not logged into the command line interface (CLI) program, press the Enter key at the User name and
password prompts. There is no default user name and password for the Switch. The administrator must first create user
names and passwords. If you have previously set up user accounts, log in and continue to configure the Switch.
12. Enter the commands to complete your desired tasks. Many commands require administrator-level access privileges. Read
the next section for more information on setting up user accounts. See the DES-3500 Series switches Command Line
Interface Reference Manual on the documentation CD for a list of all commands and additional information on using
the CLI.
13. When you have completed your tasks, exit the session with the logout command or close the emulator program.
Make sure the terminal or PC you are using to make this connection is configured to match these settings.
If you are having problems making this connection on a PC, make sure the emulation is set to VT-100. You will be able to set the
emulation by clicking on the File menu in you HyperTerminal window, clicking on Properties in the drop-down menu, and then
clicking the Settings tab. This is where you will find the Emulation options. If you still do not see anything, try rebooting the
Switch by disconnecting its powe r su ppl y .
Once connected to the console, the screen below will appear on your console screen. This is where the user will en ter commands
to perform all the available management functions. The Switch will prompt the user to enter a user name and a password. Upon
the initial connection, there is no user name or password and therefore just press enter twice to access the command line inter
face.
Figure 4- 1. Initial screen after first connection
NOTE: When you use HyperTerminal with the Microsoft® Windows® 2000 operating sys-
tem, ensure that you have Windows 2000 Service Pack 2 or later installed. Windows 2000
Service Pack 2 allows you to use arrow keys in HyperTerminal's VT100 emulation. See
www.microsoft.com for information on Windows 2000 service packs.
Page 32
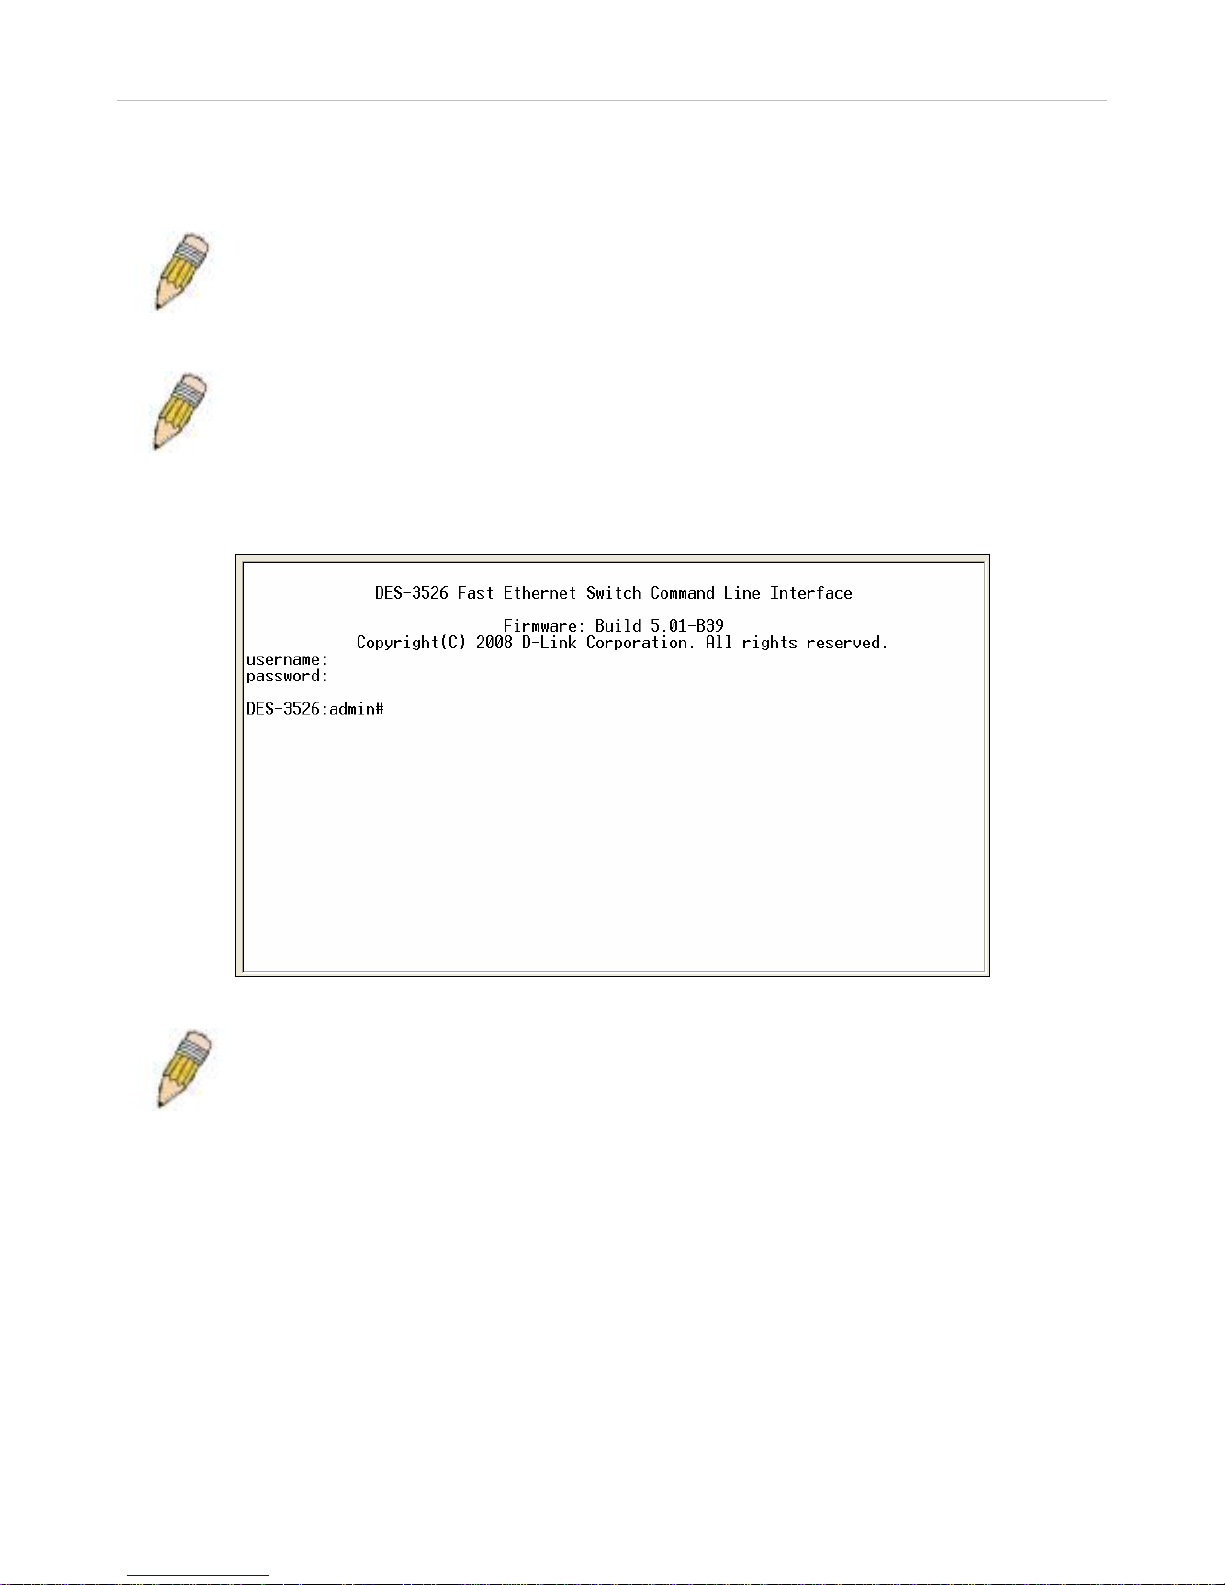
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
17
First Time Connecting to the Switch
The Switch supports user-based security that can allow you to prevent unauthorized users from accessing the Switch or changing
its settings. This section tells how to log onto the Switch.
NOTE: The passwords used to access the Switch are case-sensitive; therefore, "S" is not the same
as "s."
When you first connect to the Switch, you will be presented with the first login screen.
NOTE: Press Ctrl+R to refresh the screen. This command can be used at any time to force the
console program in the Switch to refresh the console screen.
Press Enter in both the Username and Password fields. You will be given access to the command prompt DES-3500 Series
switches:4# shown below:
There is no initial username or password. Leave the Username and Password fields blank.
Figure 4- 2. Command Prompt
NOTE: The first user automatically gets Administrator level privileges. It is recommended to create at
least one Admin-level user account for the Switch.
Password Protection
The DES-3500 Series switches do not have a default user name and password. One of the first tasks when settings up the Switch is
to create user accounts. If you log in using a predefined administrator-level user name, you have privileged access to the Switch's
management software.
After your initial login, define new passwords for both default user names to prevent unauthorized access to the Switch, and
record the passwords for future reference.
To create an administrator-level account for the Switch, do the following:
• At the CLI login prompt, enter create account admin followed by the <user name> and press the Enter key.
• You will be asked to provide a password. Type the <password> used for the administrator account being created and
press the Enter key.
• You will be prompted to enter the same password again to verify it. Type the same password and press the Enter key.
Page 33
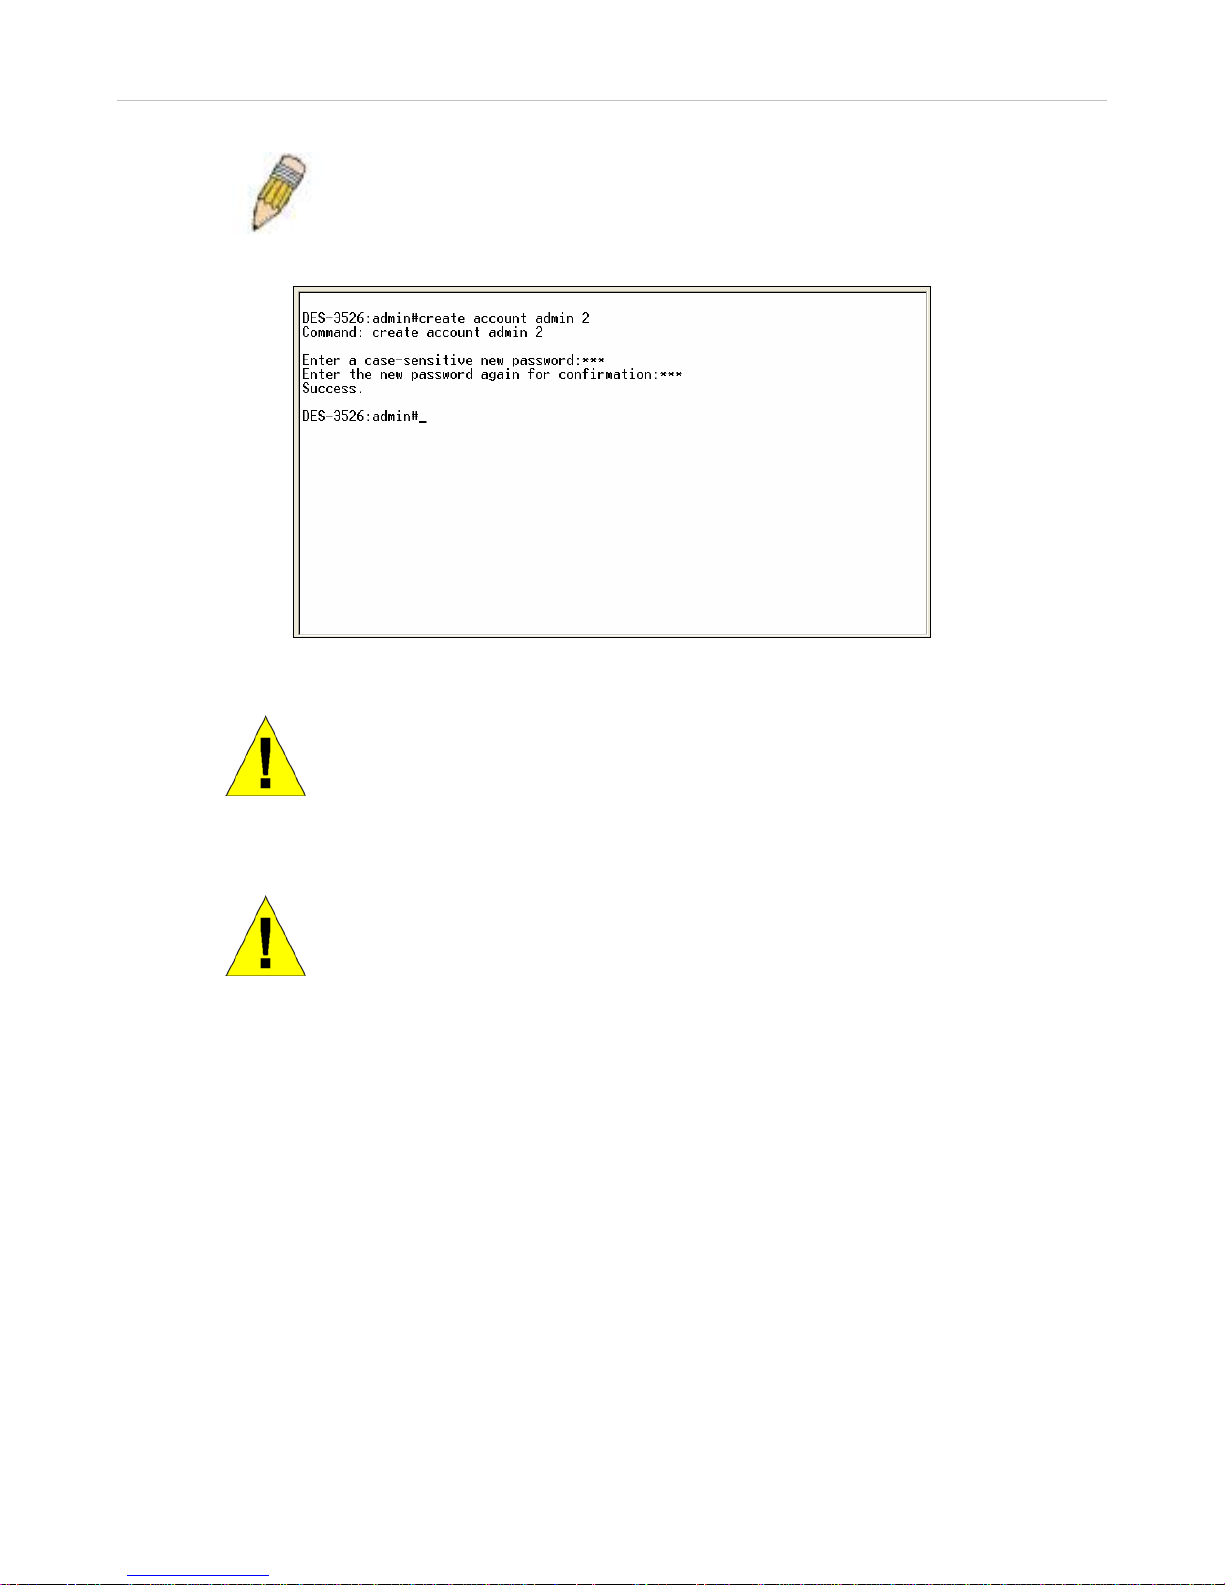
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
18
• Successful creation of the new administrator account will be verified by a Success message.
NOTE: Passwords are case sensitive. User names and passwords can be
up to 15 characters in length.
The sample below illustrates a successful creation of a new administrator-level account with the user name "newmanager".
Figure 4- 3. Create a new account
NOTICE: CLI configuration commands only modify the running configuration file
and are not saved when the Switch is rebooted. To save all your configuration
changes in nonvolatile storage, you must use the save command to copy the
running configuration file to the startup configuration.
NOTICE: In case of lost passwords or password corruption, please refer to the
D-Link website and the White Paper entitled “Password Recovery Procedure”,
which will guide you through the steps necessary to resolve this issue.
Page 34
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
19
SNMP Settings
Simple Network Management Protocol (SNMP) is an OSI Layer 7 (Application Layer) designed specifically for managing and
monitoring network devices. SNMP enables network management stations to read and modify the settings of gateways, routers,
switches, and other network devices. Use SNMP to configure system features for proper operation, monitor performance and
detect potential problems in the Switch, switch group or network.
Managed devices that support SNMP include software (referred to as an agent), which runs locally on the device. A defined set of
variables (managed objects) is maintained by the SNMP agent and used to manage the device. These objects are defined in a
Management Information Base (MIB), which provides a standard presentation of the information controlled by the on-board
SNMP agent. SNMP defines both the format of the MIB specifications and the protocol used to access this information over the
network.
The DES-3500 Series switches supports SNMP versions 1, 2c, and 3. You can specify which version of SNMP you want to use to
monitor and control the Switch. The three versions of SNMP vary in the level of security provided between the management
station and the network device.
In SNMP v.1 and v.2, user authentication is accomplished using 'community strings', which function like passwords. The remote
user SNMP application and the Switch SNMP must use the same community string. SNMP packets from any station that has not
been authenticated are ignored (dropped).
The default community strings for the Switch used for SNMP v.1 and v.2 management access are:
• public - Allows authorized management stations to retrieve MIB objects.
• private - Allows authorized management stations to retrieve and modify MIB objects.
SNMP v.3 uses a more sophisticated authentication process that is separated into two parts. The first part is to maintain a list of
users and their attributes that are allowed to act as SNMP managers. The second part describes what each user on that list can do
as an SNMP manager.
The Switch allows groups of users to be listed and configured with a shared set of privileges. The SNMP version may also be set
for a listed group of SNMP managers. Thus, you may create a group of SNMP managers that are allowed to view read-only
information or receive traps using SNMP v.1 while assigning a higher level of security to another group, granting read/write privileges using SNMP v.3.
Using SNMP v.3 individual users or groups of SNMP managers can be allowed to perform or be restricted from performing
specific SNMP management functions. The functions allowed or restricted are defined using the Object Identifier (OID)
associated with a specific MIB. An additional layer of security is available for SNMP v.3 in that SNMP messages may be
encrypted. To read more about how to configure SNMP v.3 settings for the Switch read the section entitled Management.
Traps
Traps are messages that alert network personnel of events that occur on the Switch. The events can be as serious as a reboot
(someone accidentally turned OFF the Switch), or less serious like a port status change. The Switch generates traps and sends
them to the trap recipient (or network manager). Typical traps include trap messages for Authen tication Failure, Topolog y Change
and Broadcast\Multicast Storm.
MIBs
The Switch in the Management Information Base (MIB) stores management and counter information. The Switch uses the
standard MIB-II Management Information Base module. Consequently, values for MIB objects can be retrieved from any SNMPbased network management software. In addition to the standard MIB-II, the Switch also supports its own proprietary enterprise
MIB as an extended Management Information Base. Specifying the MIB Object Identifier may also retrieve the proprietary MIB.
MIB values can be either read-only or read-write.
Page 35
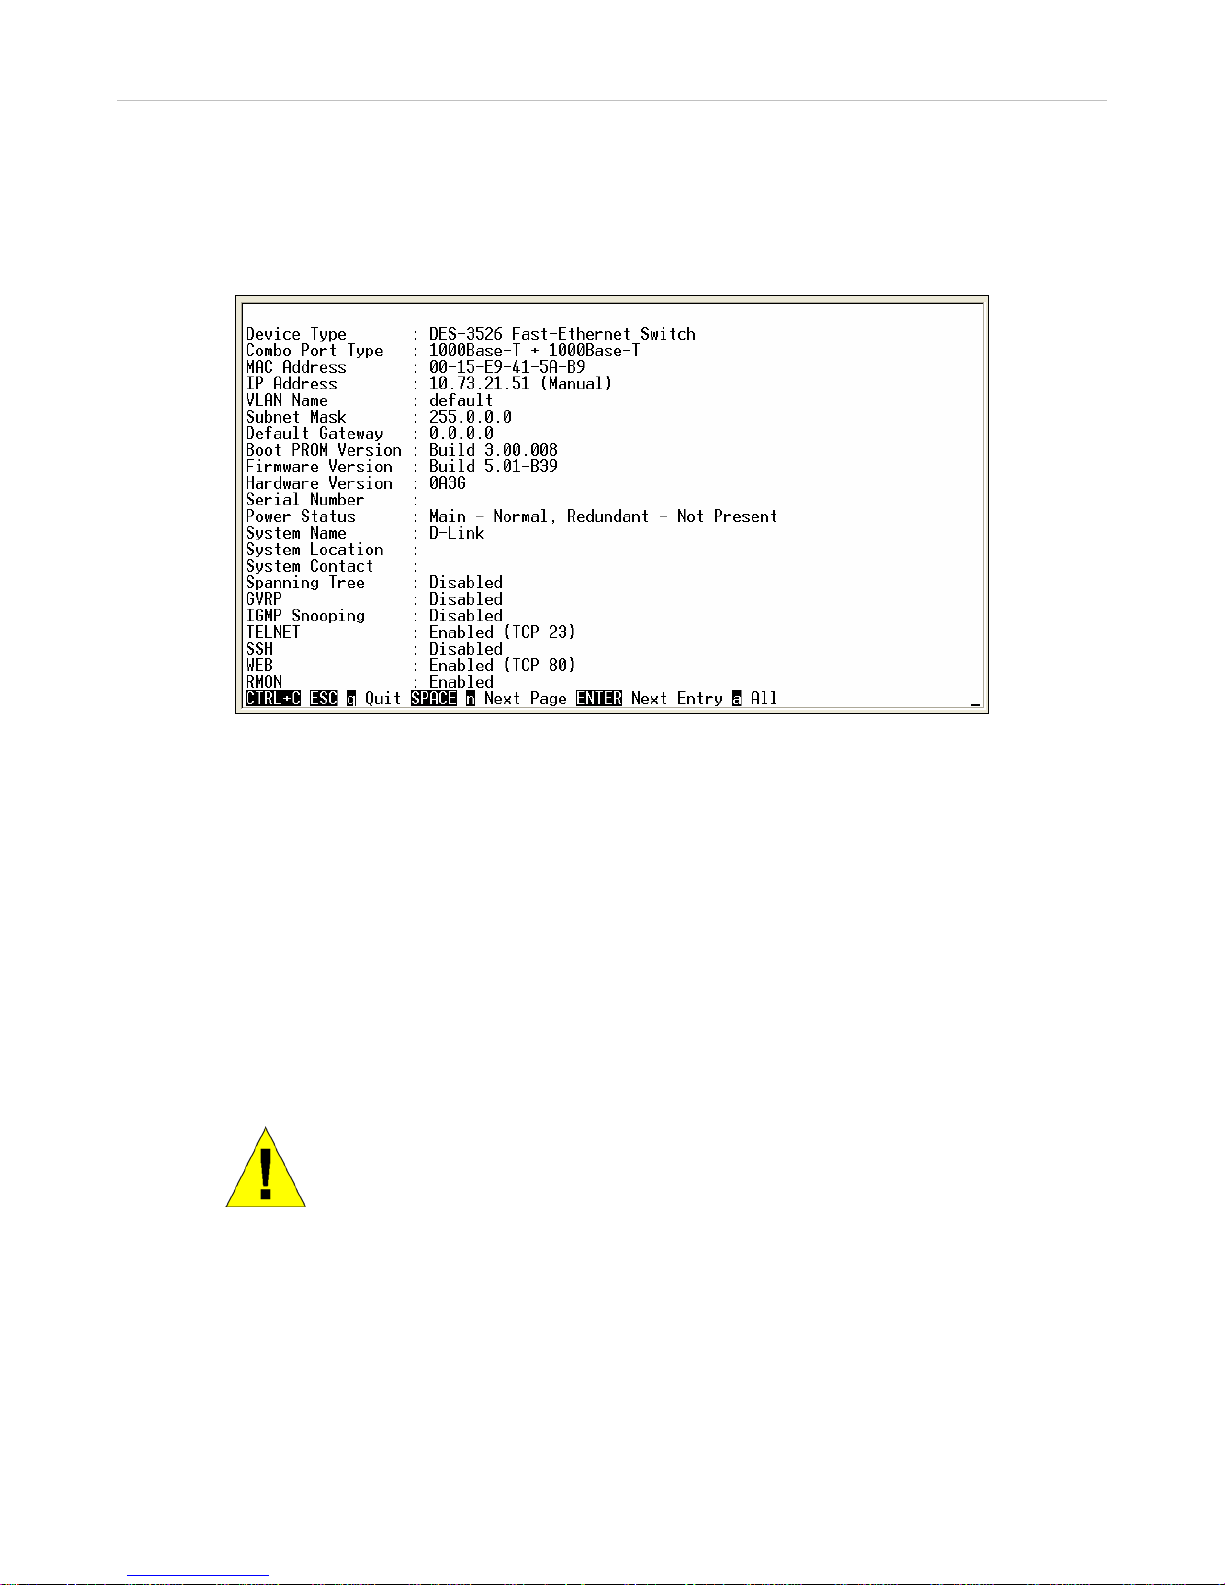
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
20
IP Address Assignment
Each Switch must be assigned its own IP Address, which is used for communication with an SNMP network manager or other
TCP/IP application (for example BOOTP, TFTP). The Switch's default IP address is 10.90.90.90. You can change the default
Switch IP address to meet the specification of your networking address scheme.
The Switch is also assigned a unique MAC address by the factory. This MAC address cannot be changed, and can be found by
entering the command "show switch" into the command line interface, as shown below.
Figure 4- 4. Show switch command
The Switch's MAC address can also be found from the Web management program on the Switch Information (Basic Settings)
window on the Configuration menu.
The IP address for the Switch must be set before it can be managed with the Web-based manager. The Switch IP address can be
automatically set using BOOTP or DHCP protocols, in which case the actual address assigned to the Switch must be known.
The IP address may be set using the Command Line Interface (CLI) over the console serial port as follows:
Starting at the command line prompt, enter the commands
config ipif System ipaddress xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy
Where the x's represen t the IP address to be assigned to the IP interface named System and th e y's represent the corresponding
subnet mask.
Alternatively, you can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x's represent the IP address to be
assigned to the IP interface named System and the z represents the corresponding number of subnets in CIDR notation.
The IP interface named System on the Switch can be assigned an IP address and subnet mask, and then be used to connect a
management station to the Switch's Telnet or Web-based management agent.
NOTICE: In case of lost passwords or password corruption, please refer to the
D-Link website and the White Paper entitled “Password Recovery Procedure”,
which will guide you through the steps necessary to resolve this issue.
Page 36
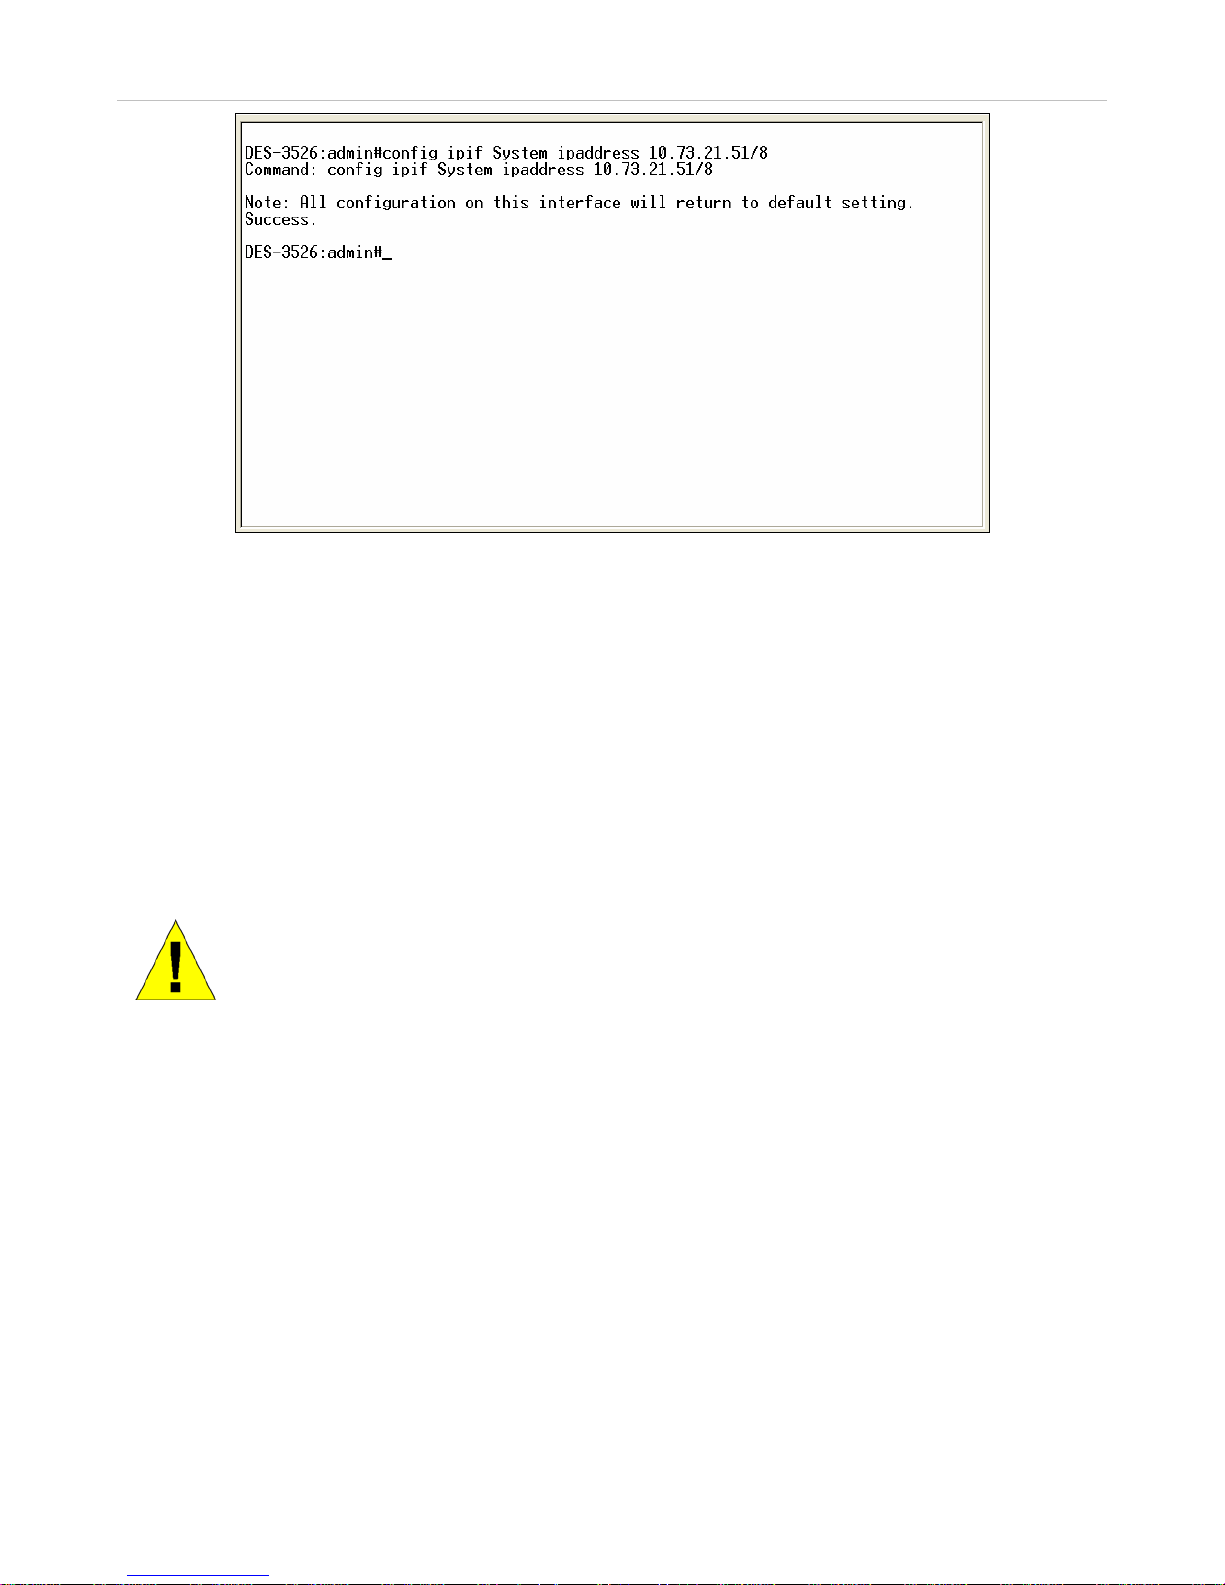
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
21
Figure 4- 5. Assigning the Switch an IP Address
In the above example, the Switch was assigned an IP address of 10.41.44.254 with a subnet mask of 255.0.0.0. The system
message Success indicates that the command was executed successfully. The Switch can now be configured and managed via
Telnet and the CLI or via the Web-based management.
Connecting Devices to the Switch
After you assign IP addresses to the Switch, you can connect devices to the Switch.
To connect a device to an SFP transceiver port:
• Use your cabling requirements to select an appropriate SFP transceiver type.
• Insert the SFP transceiver (sold separately) into the SFP transceiver slot.
• Use the appropriate network cabling to connect a device to the connectors on the SFP transceiver.
NOTICE: When the SFP transceiver acquires a link, the associated integrated 10/100/1000BASE-T
port is disabled.
Page 37
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
22
Section 5
Web-based Switch Configuration
Introduction
Login to Web manager
Web-Based User Interface
Basic Setup
Reboot
Basic Switch Setup
Network Management
Switch Utilities
Network Monitoring
IGMP Snooping Status
Introduction
All software functions of the DES-3500 Series switches can be managed, configured and monitored via the embedded web-based
(HTML) interface. The Switch can be managed from remote stations anywhere on the network through a standard browser such as
Opera, Netscape Navigator/Communicator, or Microsoft Internet Explorer. The browser acts as a universal access tool and can
communicate directly with the Switch using the HTTP protocol.
The Web-based management module and the Console program (and Telnet) are different ways to access the same internal
switching software and configure it. Thus, all settings encountered in web-based management are the same as those found in the
console program.
Login to Web Manager
To begin managing your Switch, simply run the browser you have installed on your computer and point it to the IP address you
have defined for the device. The URL in the address bar should read something like: http://123.123.123.12 3, where the numbers
123 represent the IP address of the Switch.
NOTE: The Factory default IP address for the Switch is 10.90.90.90.
This opens the management module's user authentication window, as seen below.
Page 38
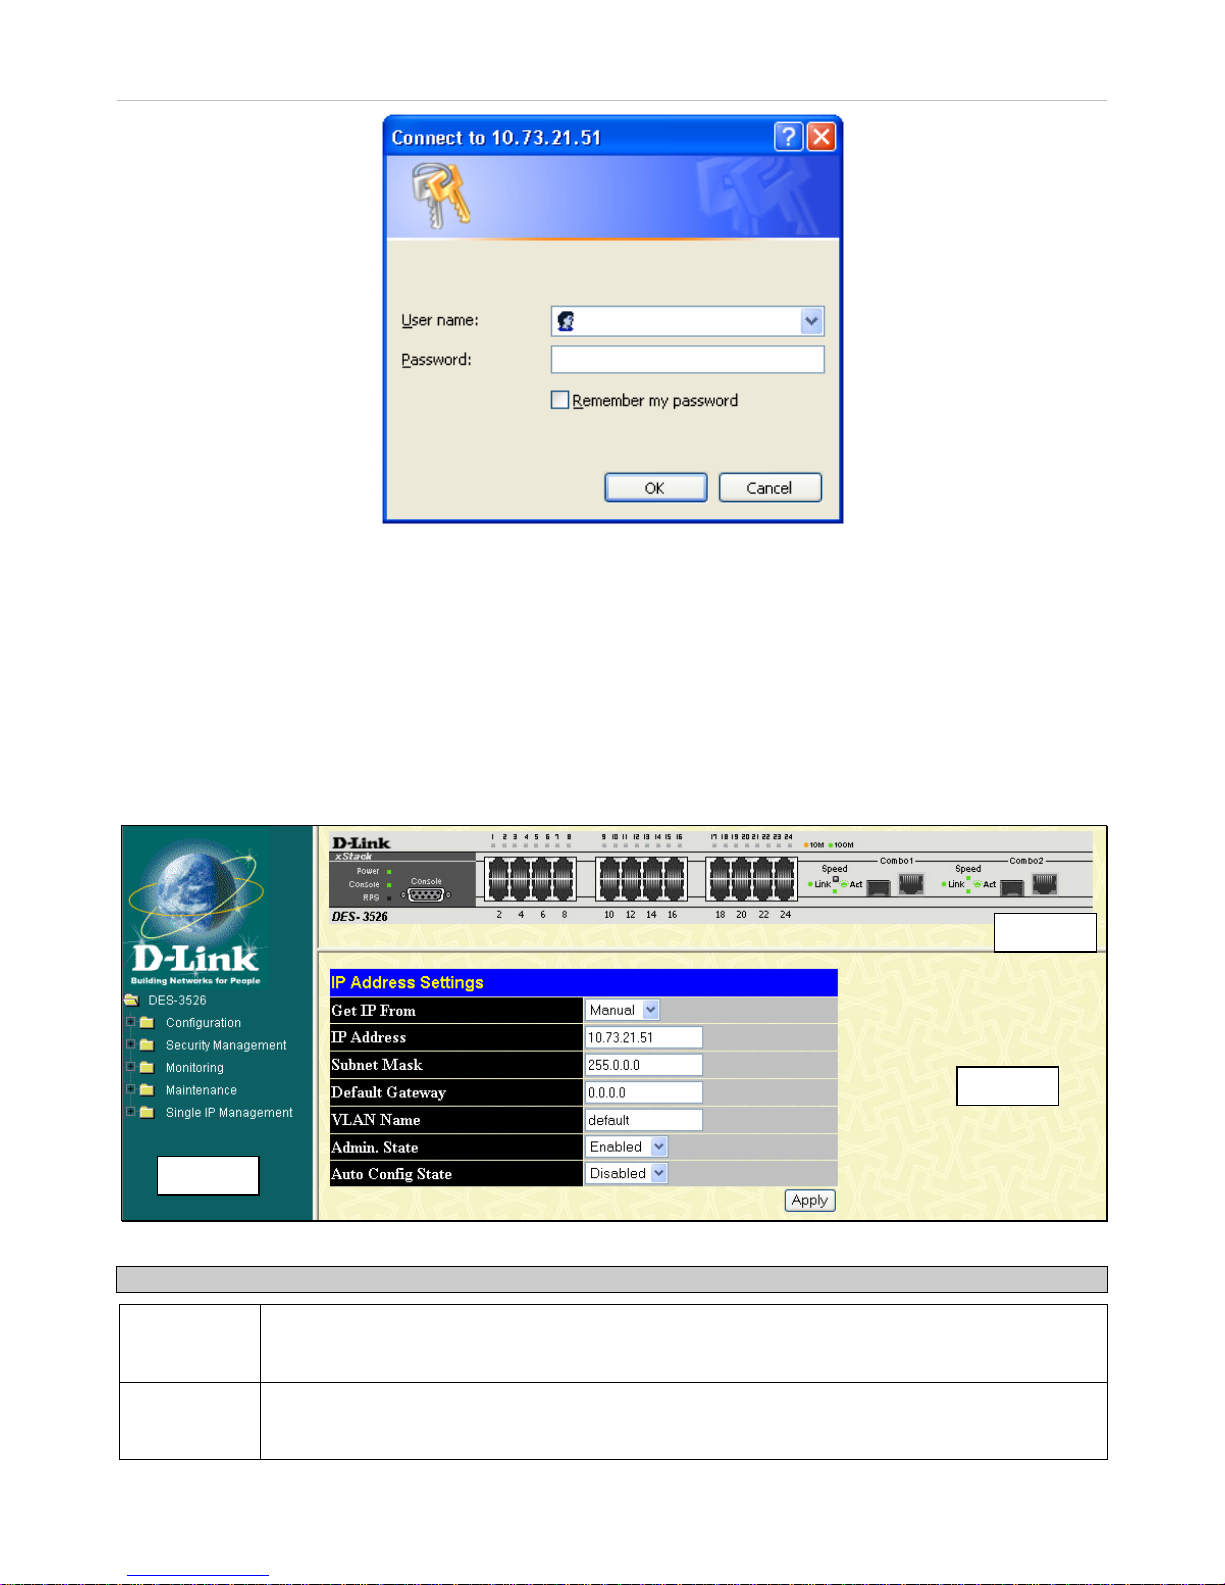
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
23
Figure 5- 1. Enter Network Password window
Leave both the User Name field and the Password field blank and click OK. This will open the Web-based user interface. The
Switch management features available in the web-based manager are explained below.
Web-based User Interface
The user interface provides access to various Switch configuration and management screens, allows you to view performance
statistics, and permits you to graphically monitor the system status.
Areas of the User Interface
The figure below shows the user interface. The user interface is divided into three distinct areas as described in the table.
Figure 5- 2. Main Web-Manager page
Area Function
Area 1
Select the menu or window to be displayed. The folder icons can be opened to display the hyperlinked menu buttons and subfolders contained within them. Click the D-Link logo to go to the D-Link
website.
Area 2
Presents a graphical near real-time image of the front panel of the Switch. This area displays the
Switch's ports and expansion modules, showing port activity, duplex mode, or flow control,
depending on the specified mode.
Area 1
Area 2
Area 3
Page 39
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
24
Various areas of the graphic can be selected for performing management functions, including port
configuration.
Area 3
Presents switch information based on your selection and the entry of configuration data.
NOTICE: Any changes made to the Switch configuration during the current session must be saved
in the Save Changes web menu (explained below) or use the command line interface (CLI)
command save.
Web Pages
When you connect to the management mode of the Switch with a web browser, a login window is displayed. Enter a user name
and password to access the Switch's management mode.
Below is a list and description of the main folders available in the web interface:
Configuration – Contains windows concerning configurations for Switch Information, IP Address, Advanced Settings, Port
Configuration, Port Description, Port Mirroring, Link Aggregation, LACP Port Setting, MAC Notification, IGMP, Spanning Tree,
Loopback Detection, Forwarding Filtering, VLANs, Traffic Control, Port Security, QoS, System Severity Settings, System Log
Server, SNTP Settings, ACL, Time Range Settings, IP-MAC Binding, Limited IP Multicast Range and Layer 3 IP Networking
and LLDP.
Security Management – Contains windows concerning configurations for Security including Trusted Host, User Accounts, Port
Access Entity, Access Authentication Control, Secure Sockets Layer (SSL), Secure Shell (SSH), SNMP Manager, Safeguard
Engine Settings, Filter and ARP Spoofing Prevention.
Monitoring – Contains windows concerning monitoring the Switch, pertaining to Port Utilization, CPU Utilization, Memory
Usage, Packets, Errors, Size, MAC Address, Switch History Log, IGMP Snooping Group, IGMP Snooping Forwarding, VLAN
Status, Router Port, Port Access Control, Layer 3 Feature, Safeguard Engine Status and Cable Diagnostics.
Maintenance – Contains windows concerning configurations and information about Switch maintenance, including TFTP
Services, Multiple Image Services, Ping Test, Save Changes, Reset, Reset System, Reset Config, Reboot Device and Logout.
Single IP Management – Contains windows concerning information on Single IP Management, including SIM Settings,
Topology, and Firmware/Configurati o n do w nloads.
NOTE: Be sure to configure the user name and password in the User Accounts menu
before connecting the Switch to the greater network.
NOTICE: In case of lost passwords or password corruption, please refer to the
D-Link website and the White Paper entitled “Password Recovery Procedure”,
which will guide you through the steps necessary to resolve this issue.
Page 40
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
25
Section 6
Configuring the Switch
Switch Information
IP Address
Advanced Settings
Port Configuration
Port Description
Port Mirroring
Link Aggregation
LACP Port Setting
MAC Notification
IGMP
Spanning Tree
Forward Filtering
VLANs
Traffic Control
Port Security
QoS
System Severity Settings
System Log Server
SNTP Settings
ACL
Time Range Settings
IP-MAC Binding
Limited IP Multicast Range Settings
Layer 3 IP Networking
LLDP
Page 41
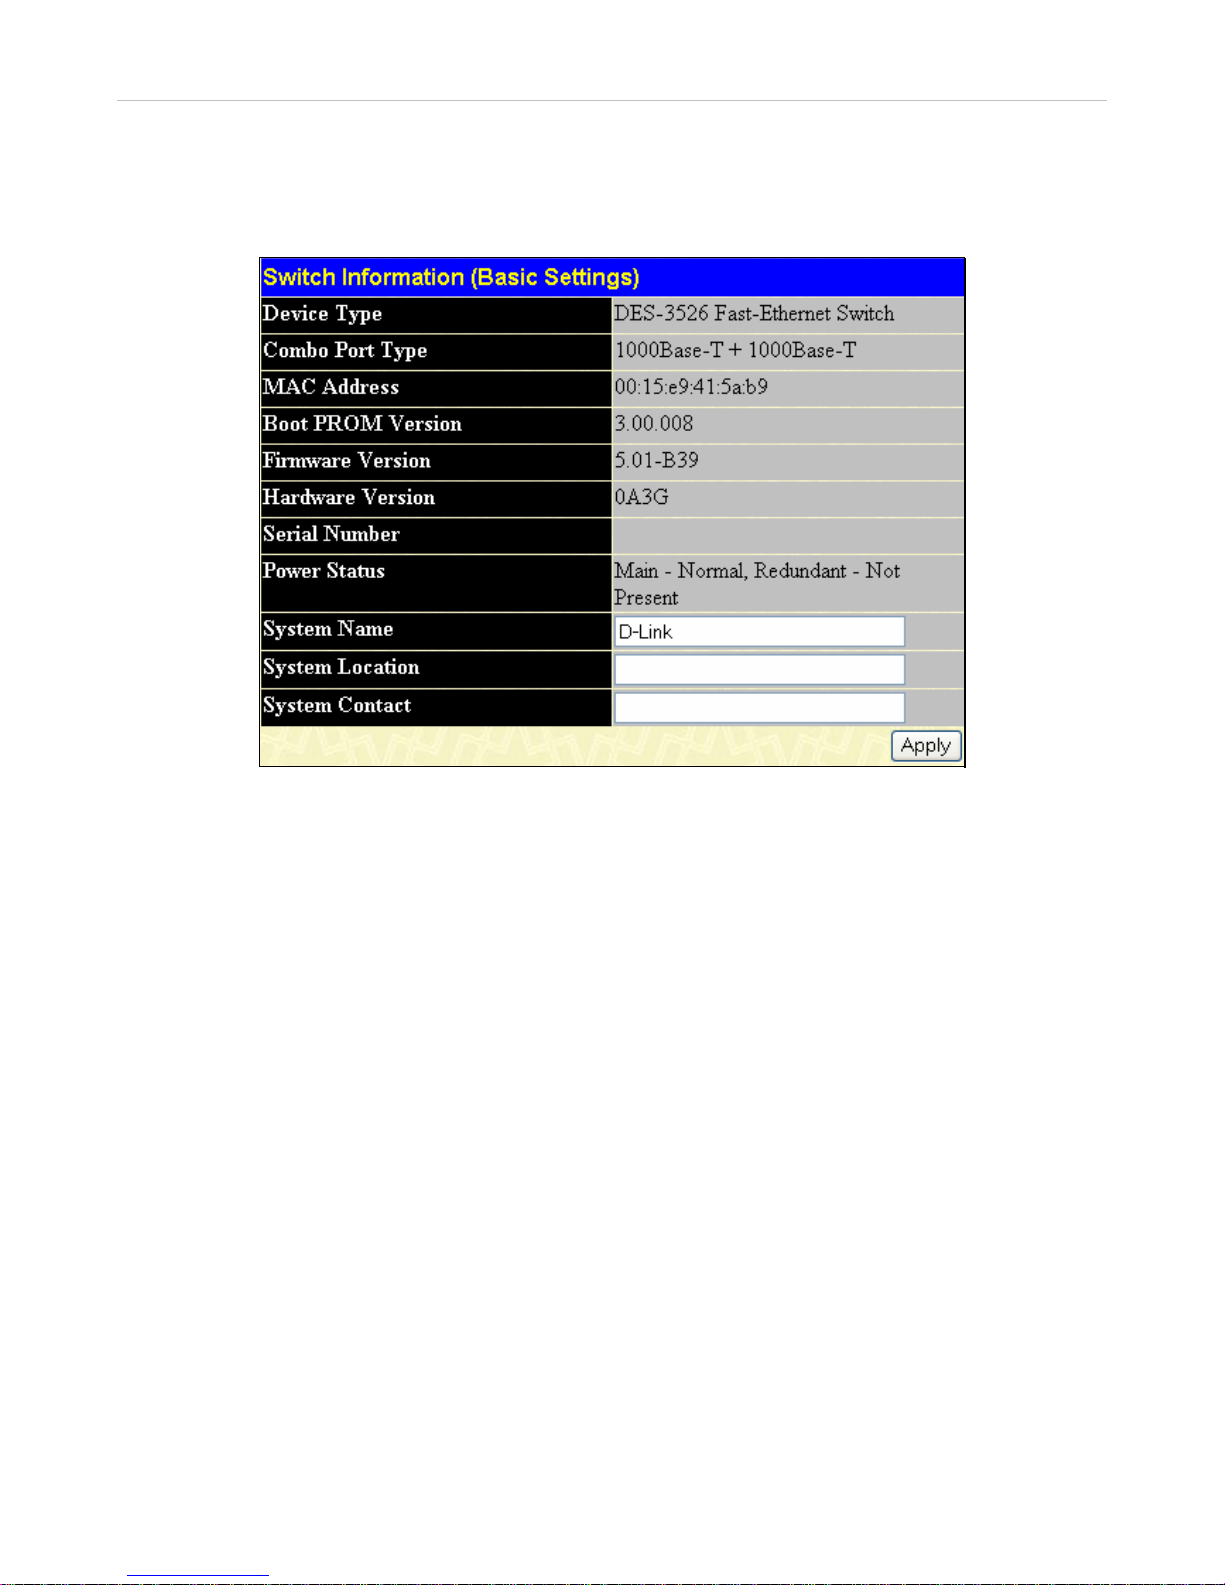
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
26
Switch Information
The subsections below describe how to change some of the basic settings for the Switch such as changing IP settings and
assigning user names and passwords for management access privileges, as well as how to save the changes and restart the Switch.
Click, Configuration > Switch Information to view the following window.
Figure 6- 1. Switch Information (Basic Settings) window
The Switch Information (Basic Settings) window shows the Switch's MAC Address (assigned by the factory and unchangeable),
the Boot PROM, Firmware Version, and Hardware Version. This information is helpful to keep track of PROM and firmware
updates and to obtain the Switch's MAC address for entry into another network device's address table, if necessary. The user may
also enter a System Name, System Location and System Contact to aid in defining the Switch, to the user's preference.
IP Address
The IP Address may initially be set using the console interface prior to connecting to it through the Ethernet. If the Switch IP
address has not yet been changed, read the introduction of the xStack
®
DES-3500 Series Command Line Interface Manual or
return to Section 4 of this manual for more information.
To change IP settings using the web manager you must access the IP Address menu located in the Configuration folder.
To configure the Switch's IP address:
Open the Configuration folder and click the IP Address menu link. The web manager will display the Switch's current IP
settings in the IP configuration menu, as seen below.
Page 42
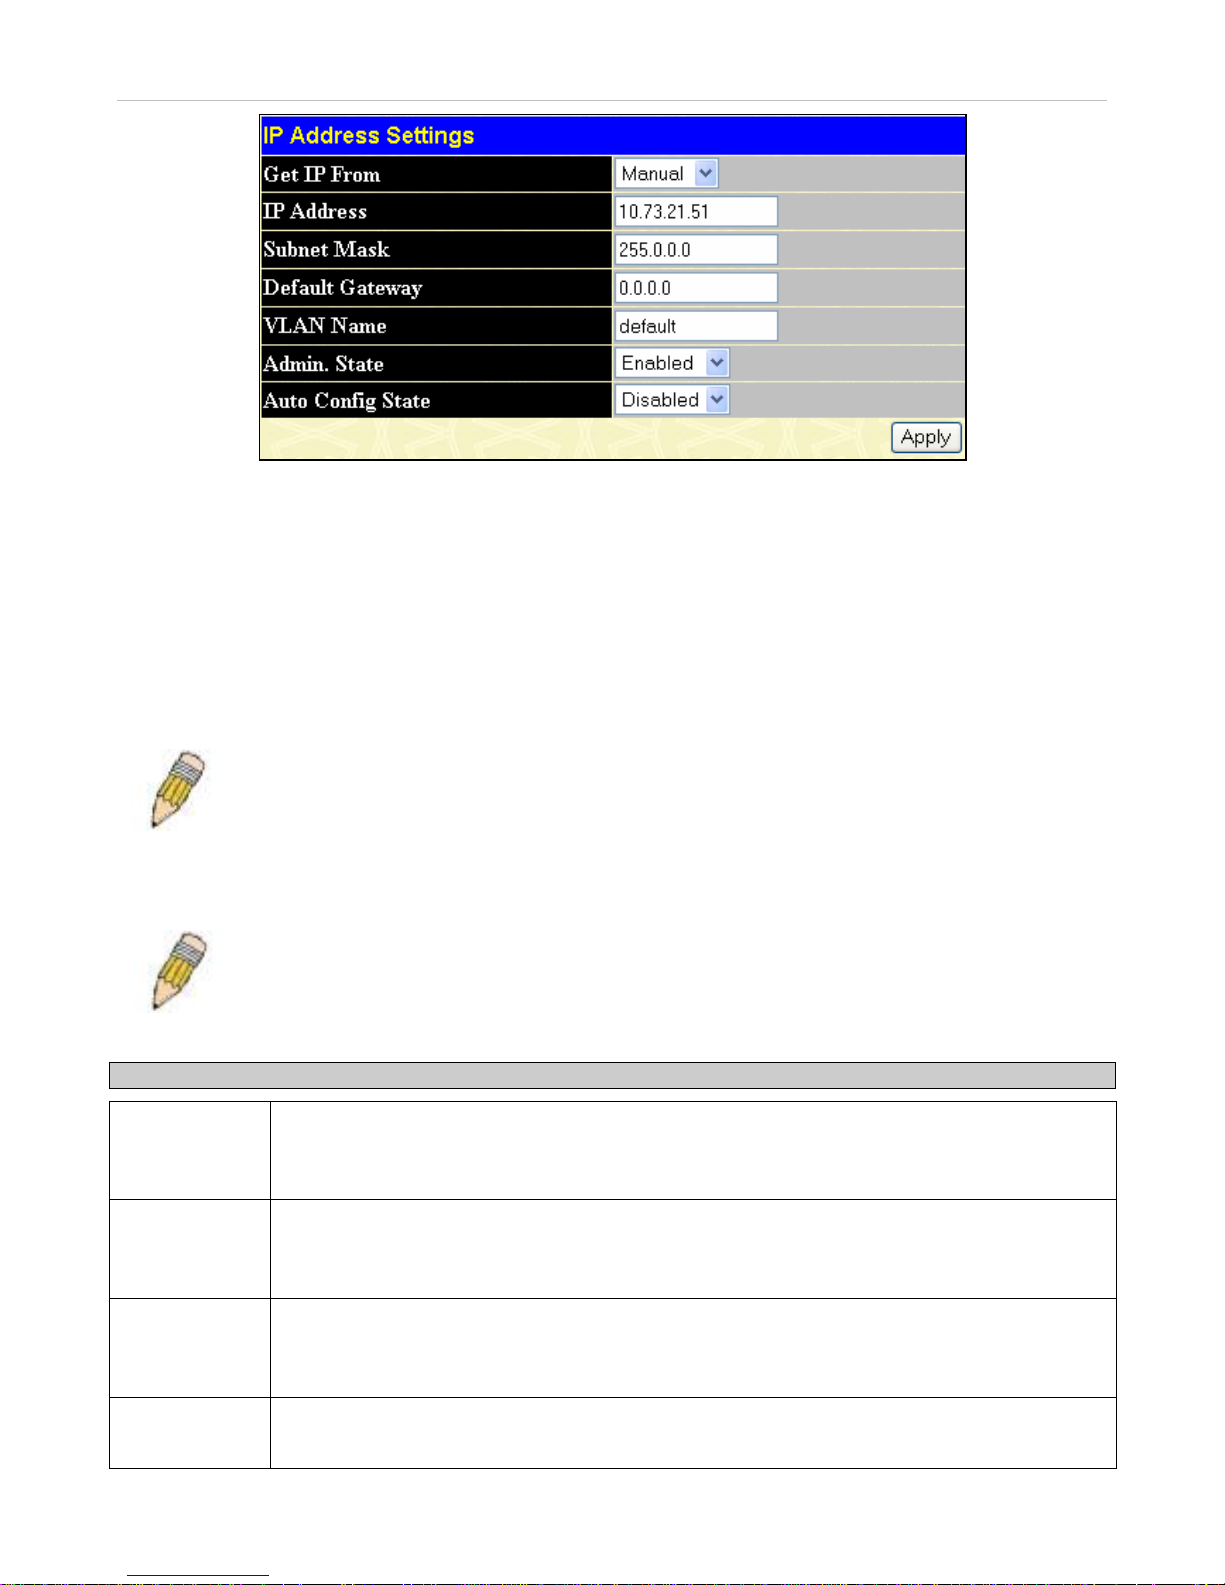
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
27
Figure 6- 2. IP Address Settings window
To manually assign the Switch's IP address, subnet mask, and default gateway address:
1. Select Manual from the Get IP From drop-down menu.
2. Enter the appropriate IP Address and Subnet Mask.
3. If you want to access the Switch from a different subnet from the one it is installed on, enter the IP address of the Default
Gateway. If you will manage the Switch from the subnet on which it is installed, you can leave the default address
(0.0.0.0) in this field.
4. If no VLANs have been previously configured on the Switch, you can use the default VLAN Name. The default VLAN
contains all of the Switch ports as members. If VLANs have been previously configured on the Switch, you will need to
enter the VLAN ID of the VLAN that contains the port connected to the management station that will access the Switch.
The Switch will allow management access from stations with the same VID listed here.
NOTE: The Switch's factory default IP address is 10.90.90.90 with a subnet mask of 255.0.0.0 and a
default gateway of 0.0.0.0.
To use the BOOTP or DHCP protocols to assign the Switch an IP address, subnet mask, and default gateway address. Use the Get
IP From pull-down menu to choose from BOOTP or DHCP. This selects how the Switch will be assigned an IP address on the
next reboot.
NOTE: If you enable the AutoConfig, the Get IP From setting will automatically become DHCP.
The IP Address Settings options are:
Parameter Description
BOOTP
The Switch will send out a BOOTP broadcast request when it is powered up. The BOOTP protocol
allows IP addresses, network masks, and default gateways to be assigned by a central BOOTP
server. If this option is set, the Switch will first look for a BOOTP server to provide it with this
information before using the default or previously entered settings.
DHCP
The Switch will send out a DHCP broadcast request when it is powered up. The DHCP protocol
allows IP addresses, network masks, and default gateways to be assigned by a DHCP server. If
this option is set, the Switch will first look for a DHCP server to provide it with this information
before using the default or previously entered settings.
Manual
Allows the entry of an IP address, Subnet Mask, and a Default Gateway for the Switch. These
fields should be of the form xxx.xxx.xxx.xxx, where each xxx is a number (represented in decimal
form) between 0 and 255. This address should be a unique address on the network assigned for
use by the network administrator.
Subnet Mask
A Bitmask that determines the extent of the subnet that the Switch is on. Should be of the form
xxx.xxx.xxx.xxx, where each xxx is a number (represented in decimal) between 0 and 255. The
value should be 255.0.0.0 for a Class A network, 255.255.0.0 for a Class B network, and
Page 43
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
28
255.255.255.0 for a Class C network, but custom subnet masks are allowed.
Default
Gateway
IP address that determines where packets with a destination address outside the current subnet
should be sent. This is usually the address of a router or a host acting as an IP gateway. If your
network is not part of an intranet, or you do not want the Switch to be accessible outside your local
network, you can leave this field unchanged.
VLAN Name
This allows the entry of a VLAN Name from which a management station will be allowed to manage
the Switch using TCP/IP (in-band via web manager or Telnet). Management stations that are on
VLANs other than the one entered here will not be able to manage the Switch in-band unless their
IP addresses are entered in the Security IP Management menu. If VLANs have not yet been
configured for the Switch, the default VLAN contains all of the Switch's ports. There are no entries
in the Security IP Management table, by default, so any management station that can connect to
the Switch can access the Switch until a management VLAN is specified or Management Station IP
Addresses are assigned.
Admin State
This allows the user to enable or disable the Admin State for the IP interface, by the using the pulldown menu. Disabling this feature will render all remote management inoperable, and thus the only
way to configure the Switch will be to use the Console port for the Command Line Interface.
Auto Config
State
When autoconfig is enabled, the Switch is instructed to get a configuration file via TFTP, and it
becomes a DHCP client automatically. The configuration file will be loaded upon booting up. In
order to use Auto Config, the DHCP server must be set up to deliver the TFTP server IP address
and configuration file name information in the DHCP reply packet. The TFTP server must be
running and have the requested configuration file stored in its base directory when the request is
received from the Switch. Consult the DHCP server and/or TFTP server software instructions for
information on loading a configuration file for use by a client. (Also see the section titled
Upload
Configuration for instructions on uploading a configuration to a TFTP server.
If the Switch is unable to complete the autoconfiguration process the previously saved
configuration file present in Switch memory will be loaded.
Click Apply to let your changes take effect.
Page 44
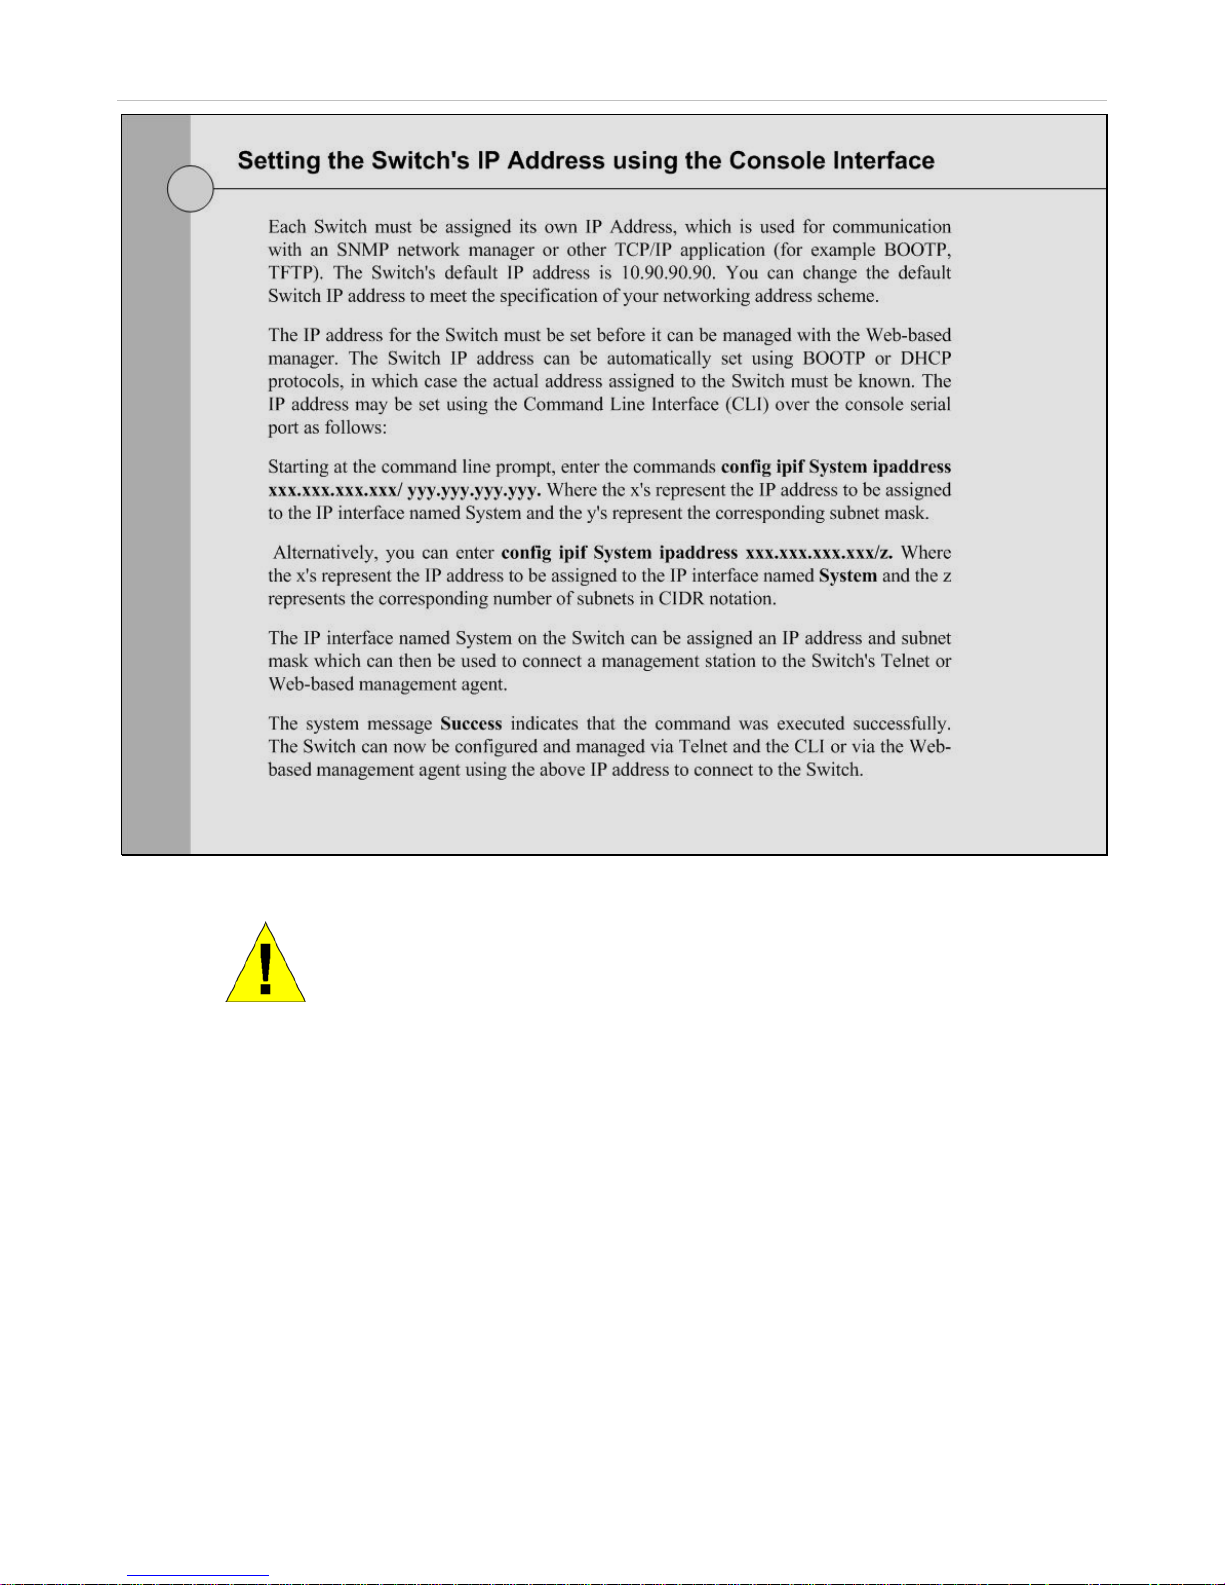
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
29
NOTICE: In case of lost passwords or password corruption, please refer to the
D-Link website and the White Paper entitled “Password Recovery Procedure”,
which will guide you through the steps necessary to resolve this issue.
Page 45
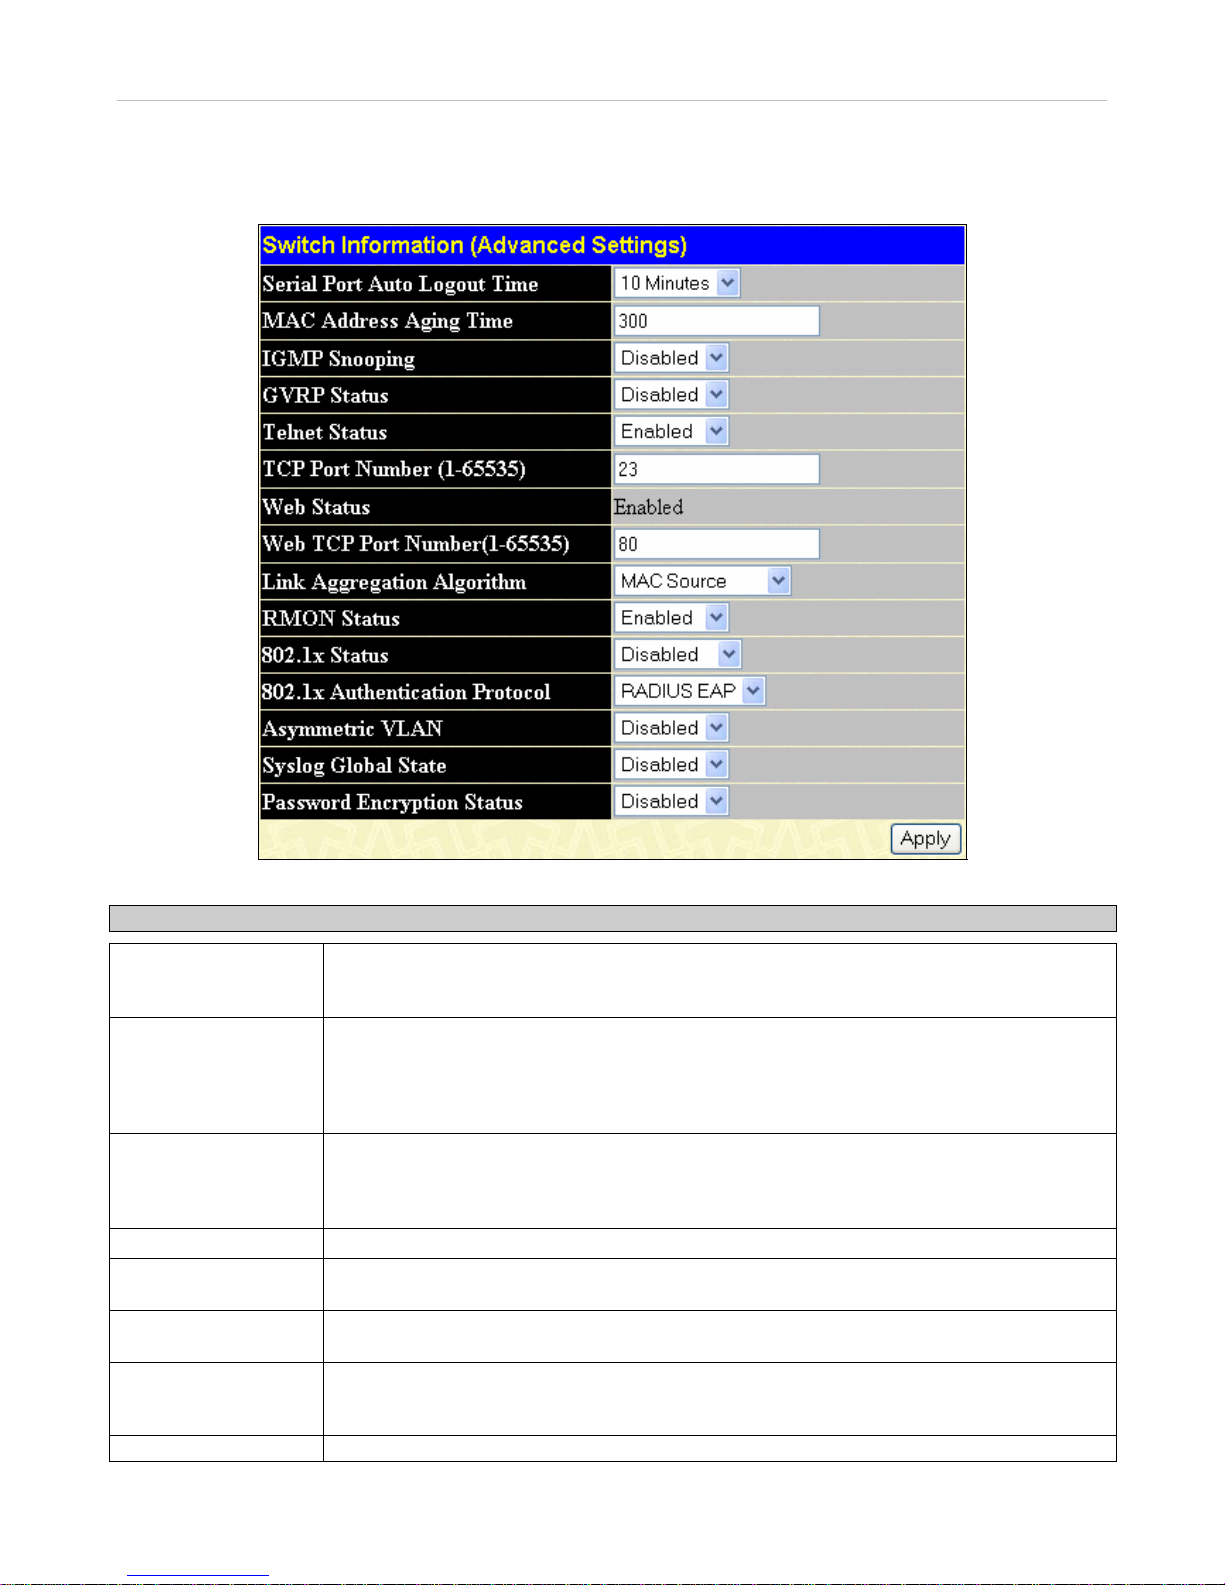
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
30
Advanced Settings
The Switch Information (Advanced Settings) window contains the main settings for all major functions for the Switch. To view
this window click, Configuration > Advanced Settings.
Figure 6- 3. Switch Information (Advanced Settings) window
Parameter Description
Serial Port Auto
Logout Time
Select the logout time used for the console interface. This automatically logs the user out
after an idle period of time, as defined. Choose from the following options: 2 Minutes, 5
Minutes, 10 Minutes, 15 Minutes or Never. The default setting is 10 minutes.
MAC Address Aging
Time
This field specifies the length of time a learned MAC Address will remain in the forwarding
table without being accessed (that is, how long a learned MAC Address is allowed to remain
idle). To change this, enter a different value representing the MAC address age-out time in
seconds. The MAC Address Aging Time can be set to any value between 10 and 1,000,000
seconds. The default setting is 300 seconds.
IGMP Snooping
To enable system-wide IGMP Snooping capability select Enabled. IGMP snooping is
Disabled by default. Enabling IGMP snooping allows you to specify use of a multicast router
only (see below). To configure IGMP Snooping for individual VLANs, use the IGMP
Snooping window under the IGMP folder.
GVRP Status
Use this pull-down menu to enable or disable GVRP on the Switch.
Telnet Status
Telnet configuration is Enabled by default. If you do not want to allow configuration of the
system through Telnet choose Disabled.
TCP Port Number (1-
65535)
The TCP port number. TCP ports are numbered between 1 and 65535. The "well-known"
TCP port for the Telnet protocol is 23.
Web Status
Web-based management is Enabled by default. If you choose to disable this by selecting
Disabled, you will lose the ability to configure the system through the web interface as soon
as these settings are applied.
Web TCP Port
The TCP port number currently being utilized by the Switch to connect to the web interface.
Page 46
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
31
Number
The "well-known" TCP port for the Web interface is 80.
Link Aggregation
Algorithm
The algorithm that the Switch uses to balance the load across the ports that make up the
port trunk group is defined by this definition. Choose MAC Source, MAC Destination, MAC
Src & Dest, IP Source, IP Destination or IP Src & Dest (See the Link Aggregation section of
this manual).
RMON Status
Remote monitoring (RMON) of the Switch is Enabled or Disabled here.
802.1x Status
MAC Address may enable by port or the Switch’s 802.1x function; the default is Disabled.
This field must be enabled to view and configure certain windows for 802.1x. More
information regarding 802.1x, its functions and implementation can be found later in this
section, under the Port Access Entity folder.
Port-Based 802.1x specifies that ports configured for 802.1x are initialized based on the port
number only and are subject to any authorization parameters configured.
MAC-based Authorization specifies that ports configured for 802.1x are initialized based on
the port number and the MAC address of the computer being authorized and are then
subject to any authorization parameters configured.
802.1x
Authentication
Protocol
The user may use the pull-down menu to choose between radius eap and radius pap for the
802.1x authentication protocol on the Switch. The default setting is radius eap.
Asymmetric VLAN
This field will enable or disable Asymmetric VLANs on the Switch. The default is Disabled.
Syslog Global State
Enables or disables Syslog State; default is Disabled.
Click Apply to implement changes made.
NOTE: When the Asymmetric VLAN function is Disabled, the user must change the VLAN setting
on the Switch to its default configurations.
Page 47
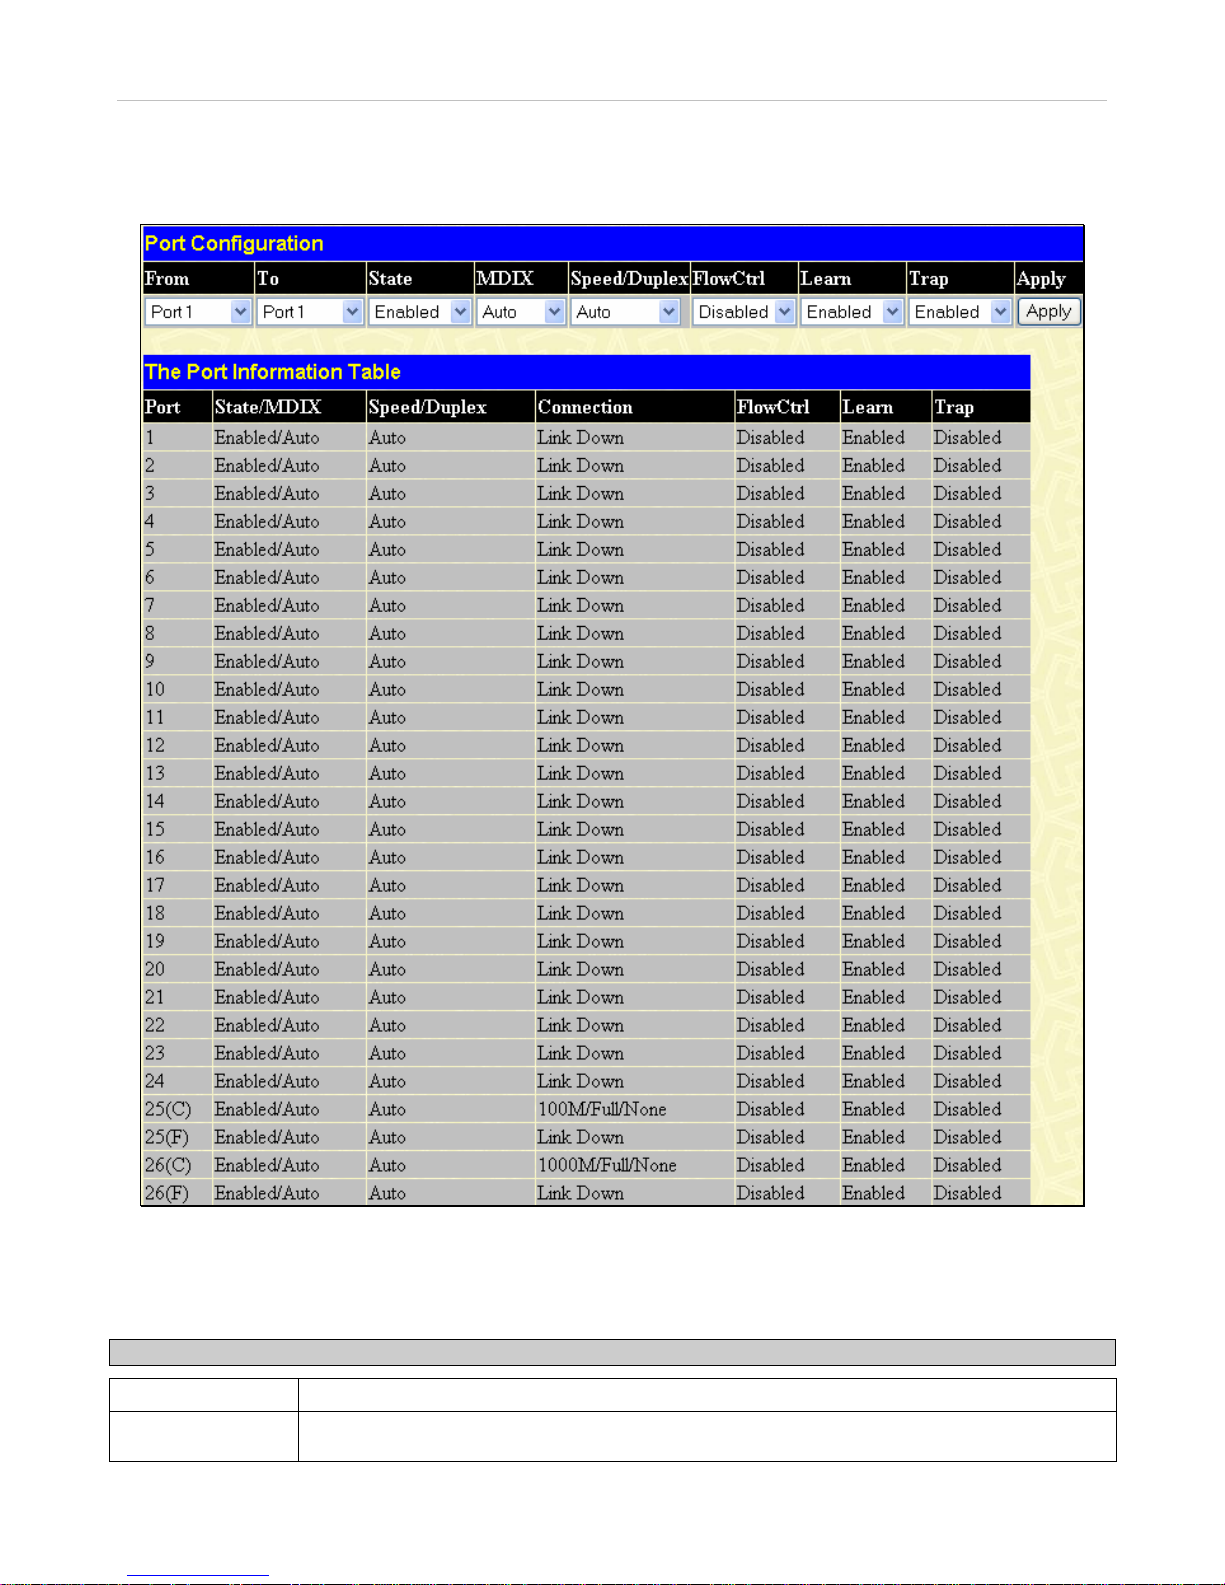
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
32
Port Configuration
This section contains information for configuring various attributes and properties for individual physical ports and Err-disabled
Ports, including port speed and flow control. To display the following window click, Configuration > Port Configuration.
Figure 6- 4. Port Configuration window
To configure switch ports:
1. Choose the port or sequential range of ports using the From…To… port pull-down menus.
2. Use the remaining pull-down menus to configure the parameters described below:
Parameter Description
State
Toggle the State field to either enable or disable a given port or group of ports.
MDIX
Medium dependent interface crossover is a female port connection on the Switch used to
connect to end stations, servers and hubs. The drop down menu allows the user to choose
Page 48
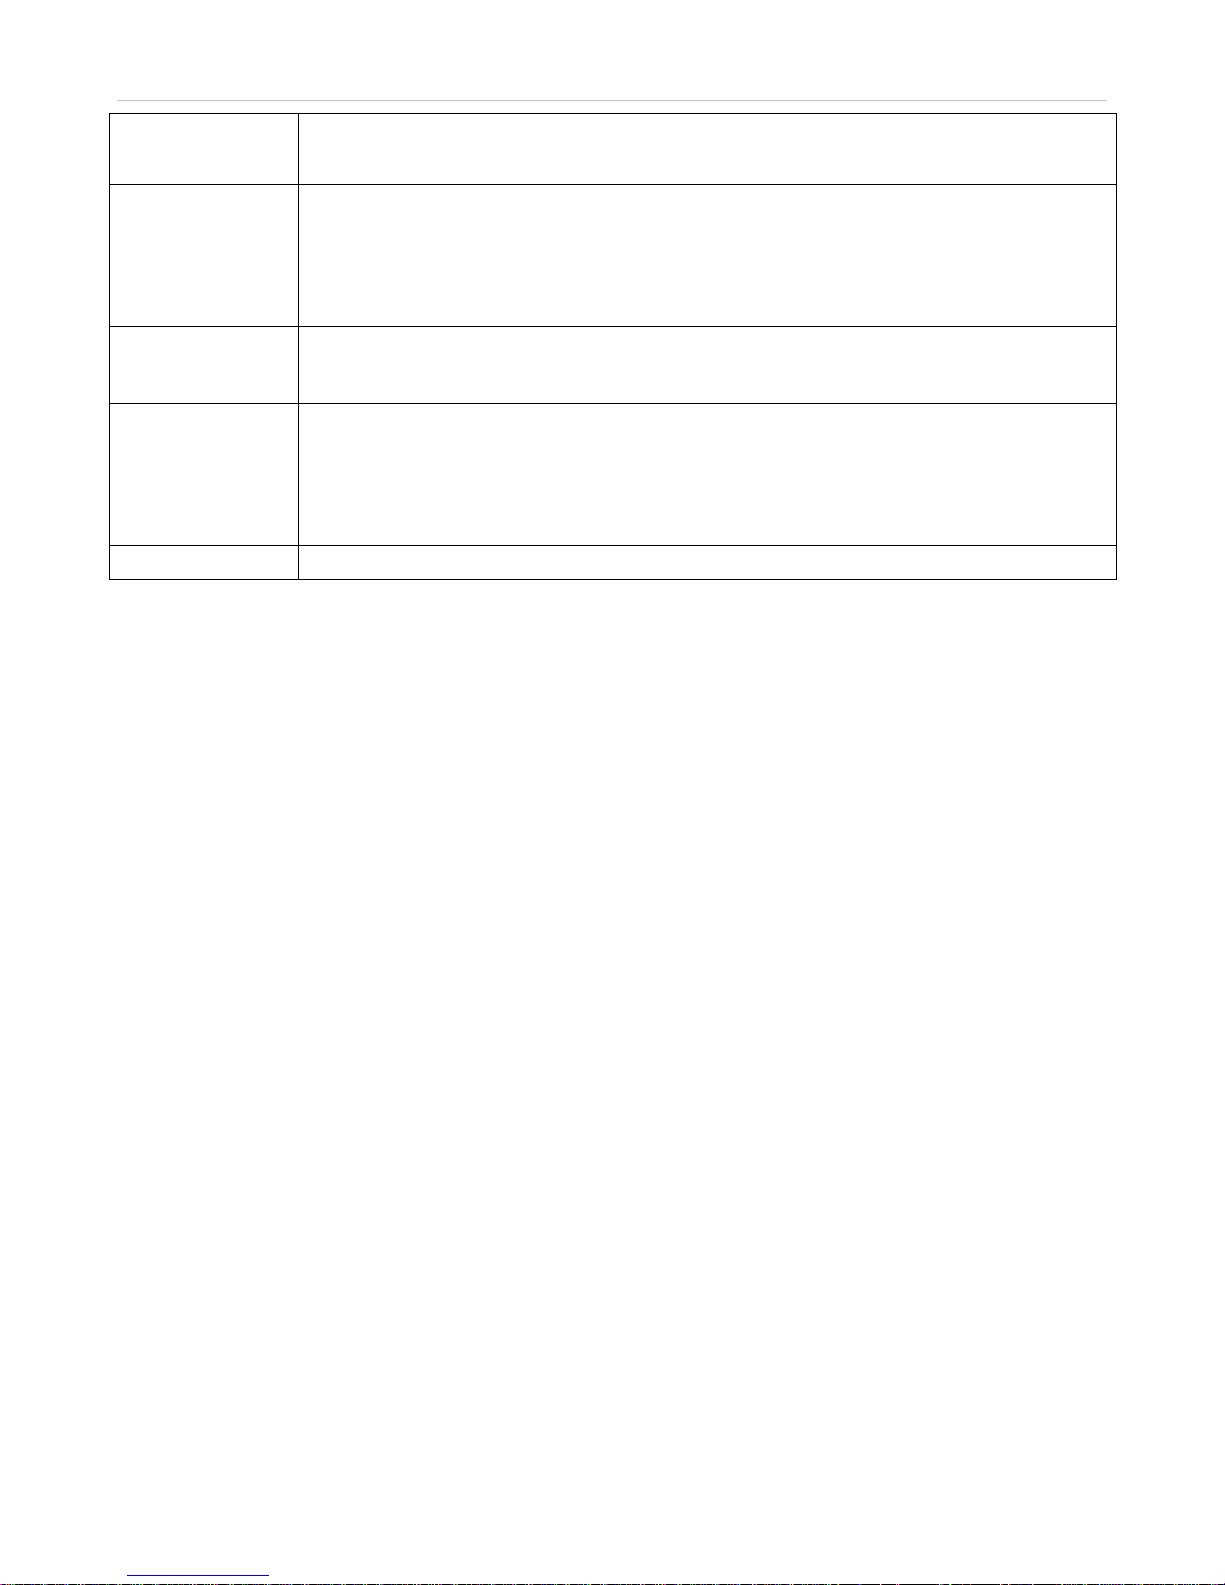
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
33
between Auto, Normal or Cross. Auto will automatically switch to the proper configuration once
a cable is connected. Normal will be selected if a straight-through cable is being used and
Cross should be selected if a crossover cable is being used.
Speed/Duplex
Toggle the Speed/Duplex field to either select the speed and duplex/half-duplex state of the
port. Auto denotes auto-negotiation between 10 and 100 Mbps devices, in full- or half-duplex.
The Auto setting allows the port to automatically determine the fastest settings the device the
port is connected to can handle, and then to use those settings. The other options are Auto,
10M/Half, 10M/Full, 100M/Half, 100M/Full, and 1000M/Full. There is no automatic adjustment of
port settings with any option other than Auto.
Flow Control
Displays the flow control scheme used for the various port configurations. Ports configured for
full-duplex use 802.3x flow control, half-duplex ports use backpressure flow control, and Auto
ports use an automatic selection of the two. The default is Disabled.
Learn
Enable or disable MAC address learning for the selected ports. When Enabled, destination and
source MAC addresses are automatically listed in the forwarding table. When learning is Dis-
abled, MAC addresses must be manually entered into the forwarding table. This is sometimes
done for reasons of security or efficiency. See the section on Forwarding/Filtering for
information on entering MAC addresses into the forwarding table. The default setting is
Disabled.
Trap
Enables or disables trap support on the switch. The default setting is Disabled.
Click Apply to implement the new settings on the Switch.
Page 49
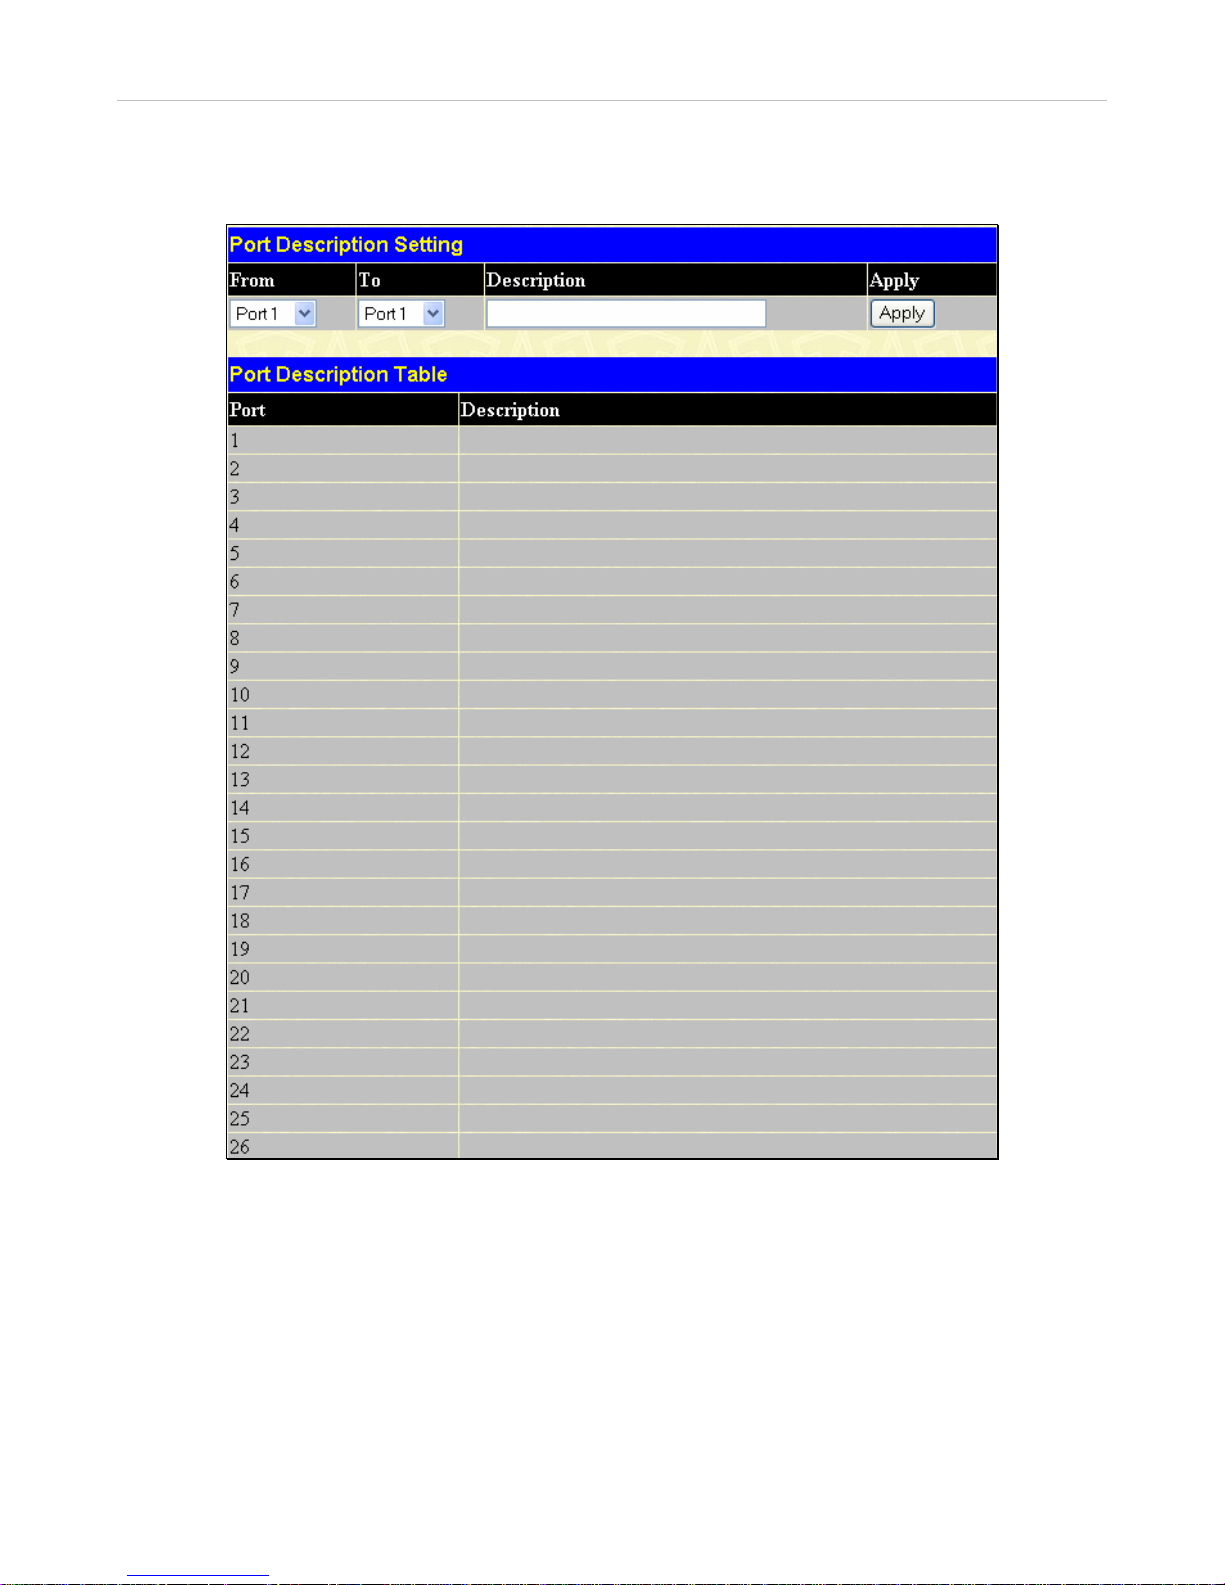
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
34
Port Description
The DES-3500 Series switches support a port description feature where the user may name various ports on the Switch. To assign
names to various ports, click Configuration > Port Description:
Figure 6- 5. Port Description Settings window
Use the From and To pull down menu to choose a port or range of ports and enter a description of the port(s). Click Apply to set
the descriptions in the Port Description Table.
Page 50
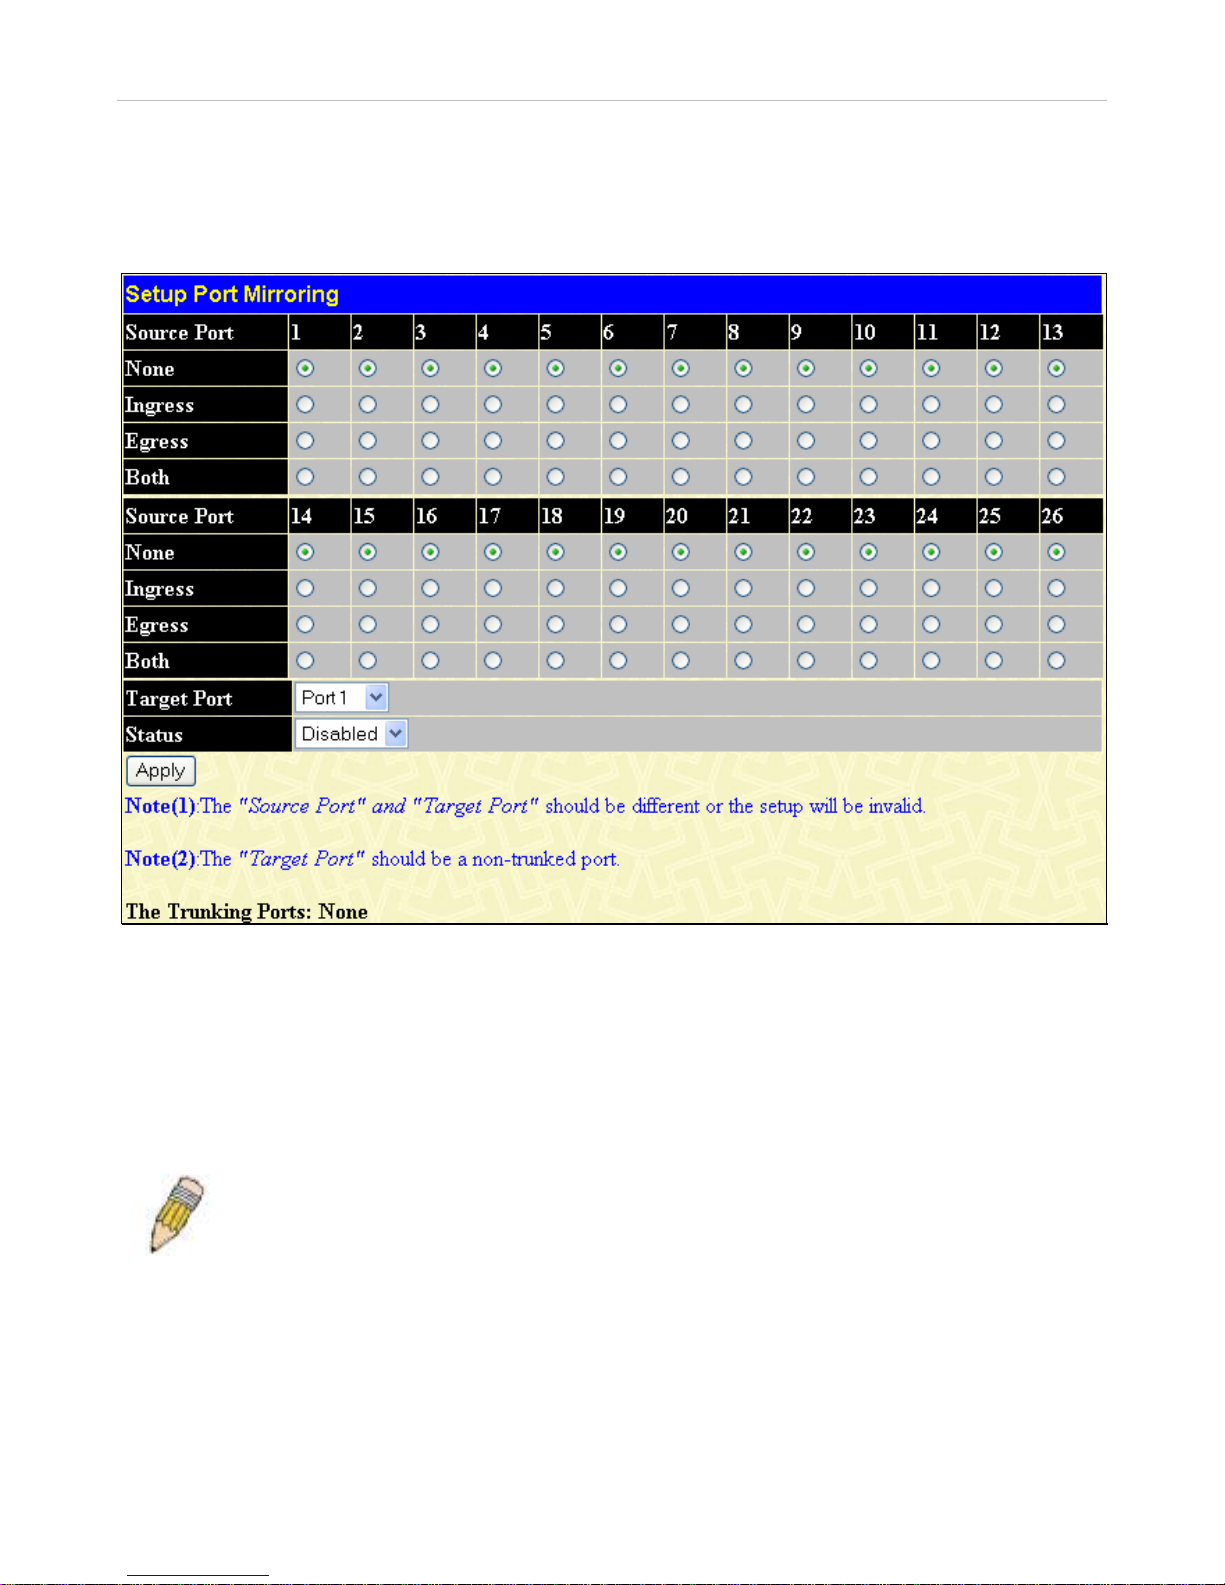
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
35
Port Mirroring
The Switch allows you to copy frames transmitted and received on a port and redirect the copies to another port. You can attach a
monitoring device to the mirrored port, such as a sniffer or an RMON probe, to view details about the packets passing through the
first port. This is useful for network monitoring and troubleshooting purposes. To view the Port Mirroring window, click
Configuration > Port Mirroring.
Figure 6- 6. Setup Port Mirroring window
To configure a mirror port:
• Select the Source Port from where you want to copy frames and the Target Port, which receives the copies from the
source port.
• Select the Source Direction, Ingress, Egress, or Both and change the Status drop-down menu to Enabled.
• Click Apply to let the changes take effect.
NOTE: You cannot mirror a fast port onto a slower port. For example, if you try to mirror the traffic
from a 100 Mbps port onto a 10 Mbps port, this can cause throughput problems. The port you are
copying frames from should always support an equal or lower speed than the port to which you are
sending the copies. Also, the target port for the mirroring cannot be a member of a trunk group.
Please note a target port and a source port cannot be the same port.
Page 51
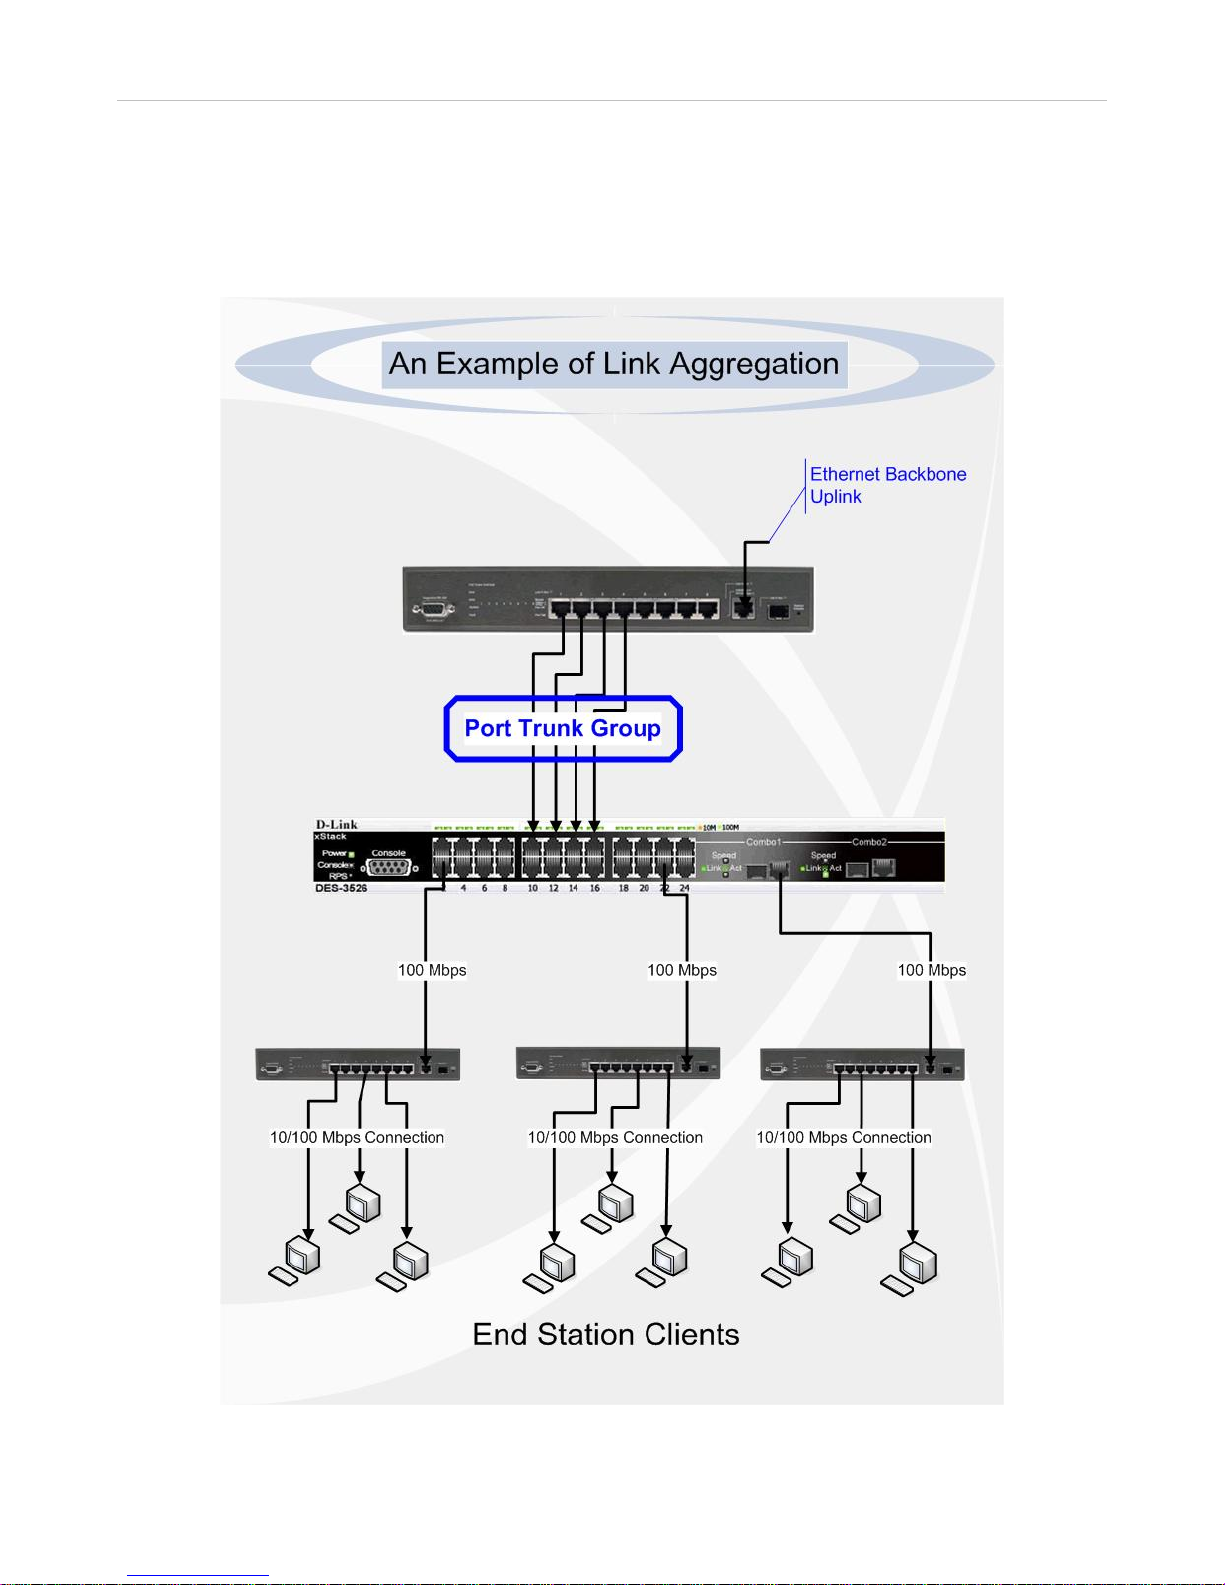
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
36
Link Aggregation
Understanding Port Trunk Groups
Port trunk groups are used to combine a number of ports together to make a single high-bandwidth data pipeline.
The DES-3500 Series switches support up to six port trunk groups with 2 to 8 ports in each group. A potential bit rate of 8000
Mbps can be achieved.
Figure 6- 7. Example of Port Trunk Group
Page 52
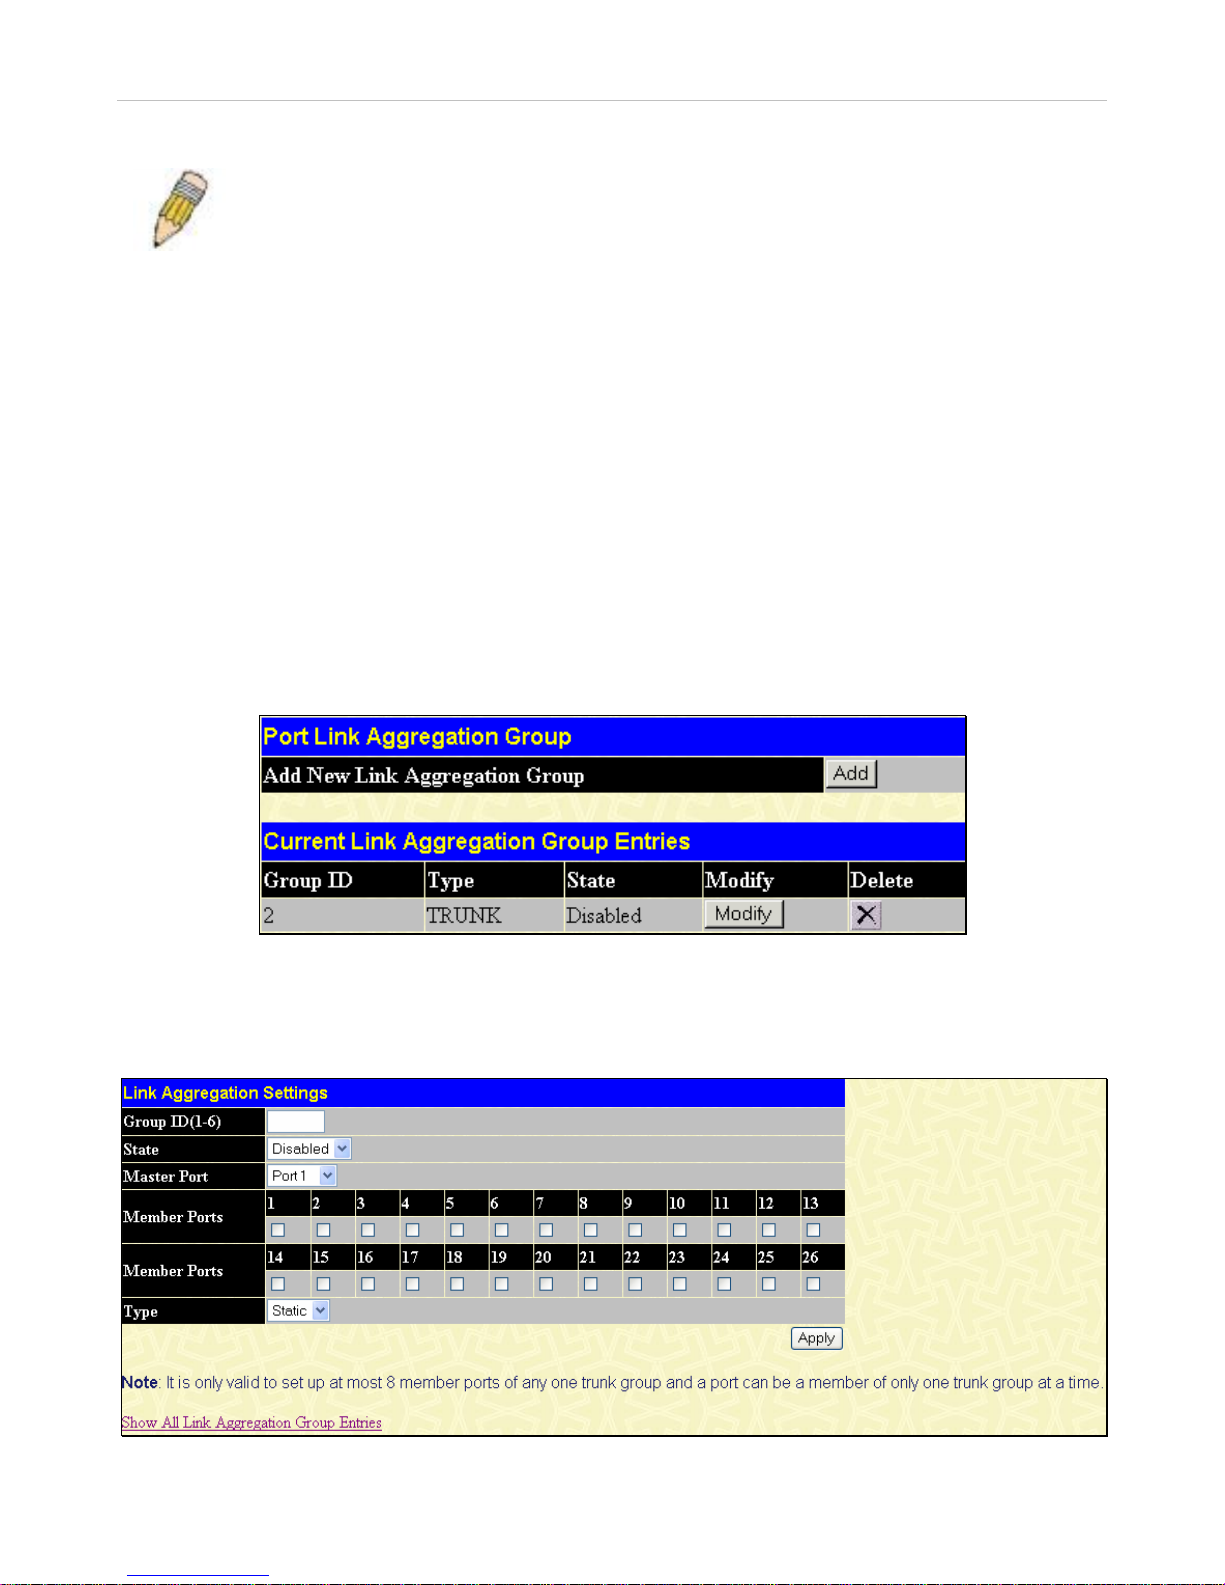
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
37
The Switch treats all ports in a trunk group as a single port. Data transmitted to a specific host (destination address) will always be
transmitted over the same port in a trunk group. This allows packets in a data stream to arrive in the same order they were sent.
NOTE: If any ports within the trunk group become disconnected, packets intended for the disconnected port will be load shared among the other unlinked ports of the link aggregation group.
Link aggregation allows several ports to be grouped together and to act as a single link. This gives a bandwidth that is a multiple
of a single link's bandwidth.
Link aggregation is most commonly used to link a bandwidth intensive network device or devices, such as a server, to the
backbone of a network.
The Switch allows the creation of up to six link aggregation groups, each group consisting of 2 to 8 links (ports). The aggregated
links must be contiguous (they must have sequential port numbers) except the two (optional) Gigabit ports, which can only belong
to a single link aggregation group. All of the ports in the group must be members of the same VLAN, and their STP status, static
multicast, traffic control; traffic segmentation and 802.1p default priority configurations must be identical. Port locking, port
mirroring and 802.1X must not be enabled on the trunk group . Further, the aggregated links must all be of the same speed and
should be configured as full duplex.
The Master Port of the group is to be configured by the user, and all configuration options, including the VLAN configuration that
can be applied to the Master Port, are applied to the entire link aggregation group.
Load balancing is automatically applied to the ports in the aggregated group, and a link failure within the group causes the
network traffic to be directed to the remaining links in the group.
The Spanning Tree Protocol will treat a link aggregation group as a single link, on the switch level. On th e port leve l, the ST P will
use the port parameters of the Master Port in the calculation of port cost and in determining the state of the link aggregation group.
If two redundant link aggregation group s are configured on the Switch, STP will block one entire group; in the same way STP will
block a single port that has a redundant link.
To configure port trunking, click Configuration > Link Aggregation to view the following window:
Figure 6- 8. Port Link Aggregation Group window
To configure port trunk groups, click the Add button to add a new tru nk group and use the Link Aggregation Settings window
(see example below) to set up trunk groups. To modify a port trunk group, click the Modify bu tton corr espond ing to the entr y you
wish to alter. To delete a port trunk group, click the corresponding X under the Delete heading in the Current Link Aggregation
Group Entries table.
Figure 6- 9. Link Aggregation Settings window – Add
Page 53
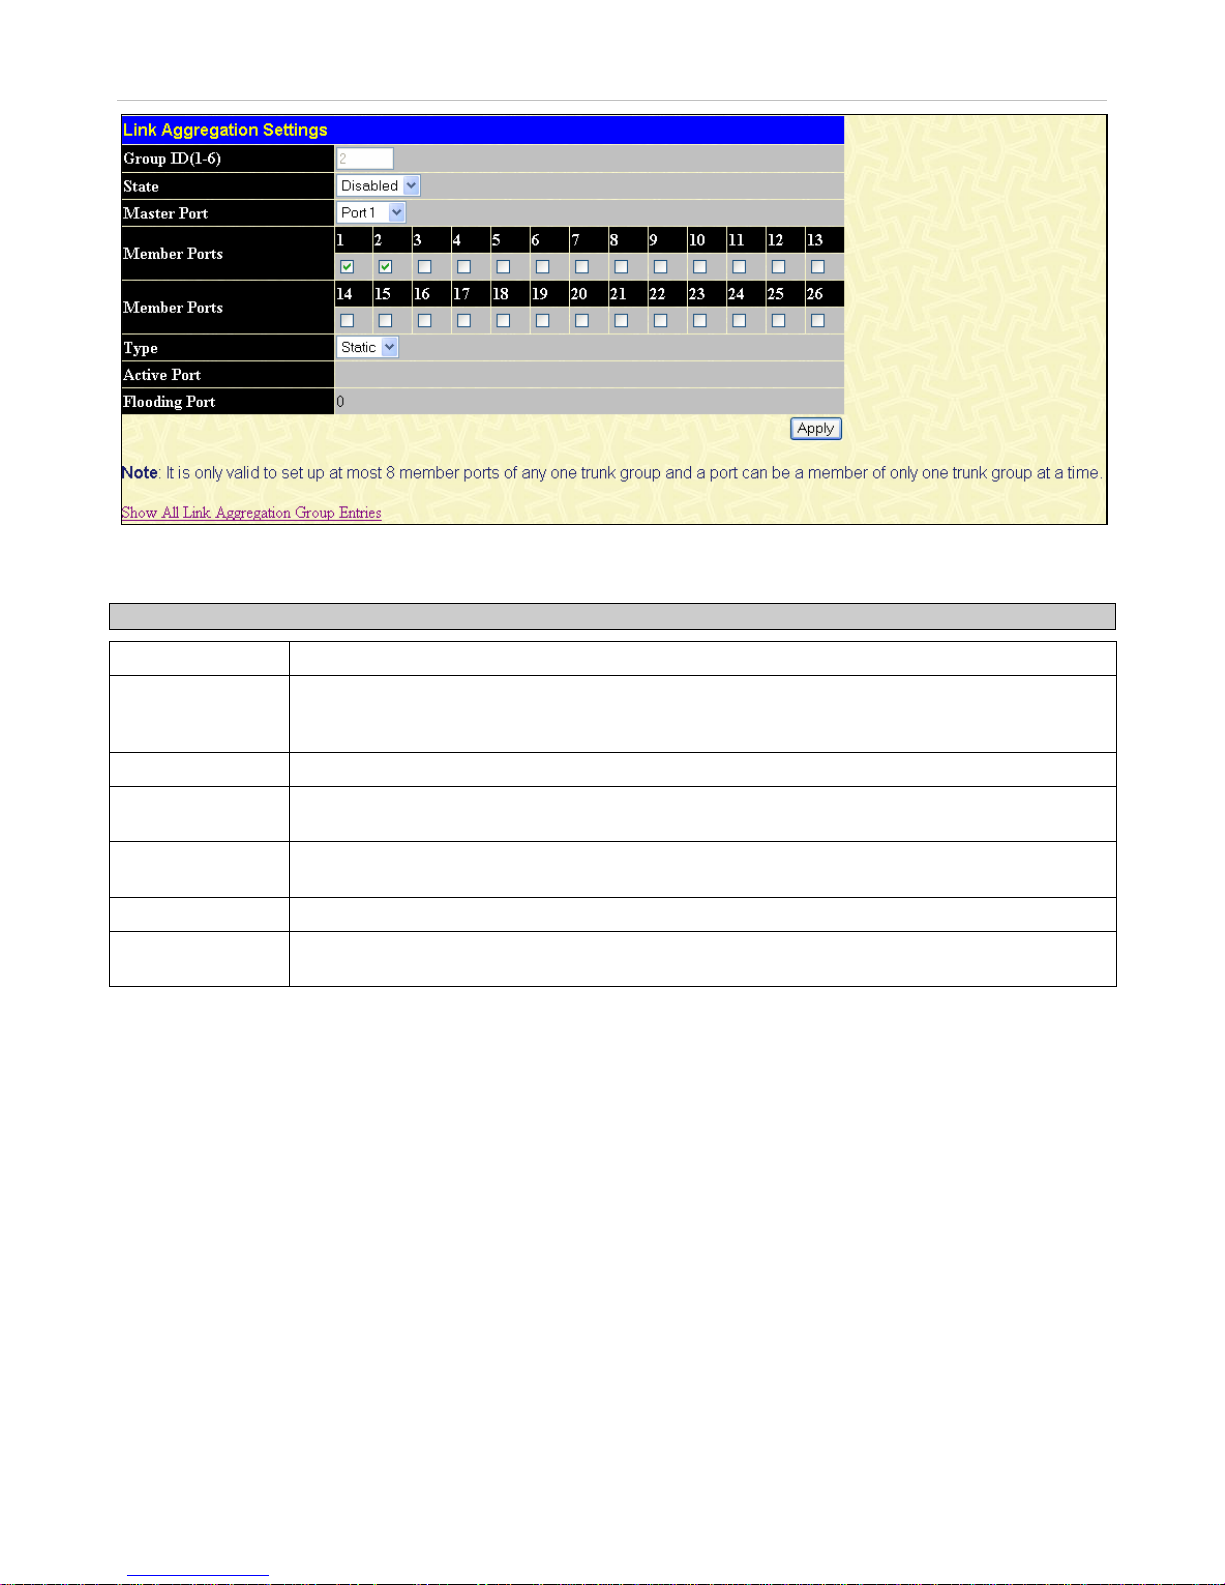
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
38
Figure 6- 10. Link Aggregation Settings window - Modify
The user-changeable parameters are as follows:
Parameter Description
Group ID
Select an ID number for the group, between 1 and 6.
State
Trunk groups can be toggled between Enabled and Disabled. This is used to turn a port trunking
group on or off. This is useful for diagnostics, to quickly isolate a bandwidth intensive network
device or to have an absolute backup aggregation group that is not under automatic control.
Master Port
Choose the Master Port for the trunk group using the pull-down menu.
Member Ports
Choose the members of a trunked group. Up to eight ports per group can be assigned to a
group.
Flooding Port
A trunking group must designate one port to allow transmission of broadcasts and unknown
unicasts.
Active Port
Shows the port that is currently forwarding packets.
Type
This pull-down menu allows you to select between Static and LACP (Link Aggregation Control
Protocol). LACP allows for the automatic detection of links in a Port Trunking Group.
After setting the previous parameters, click Apply to allow your changes to be implemented. Successfully created trunk groups
will be show in the Current Link Aggregation Group Entries table as seen in Figure 6-8.
Page 54
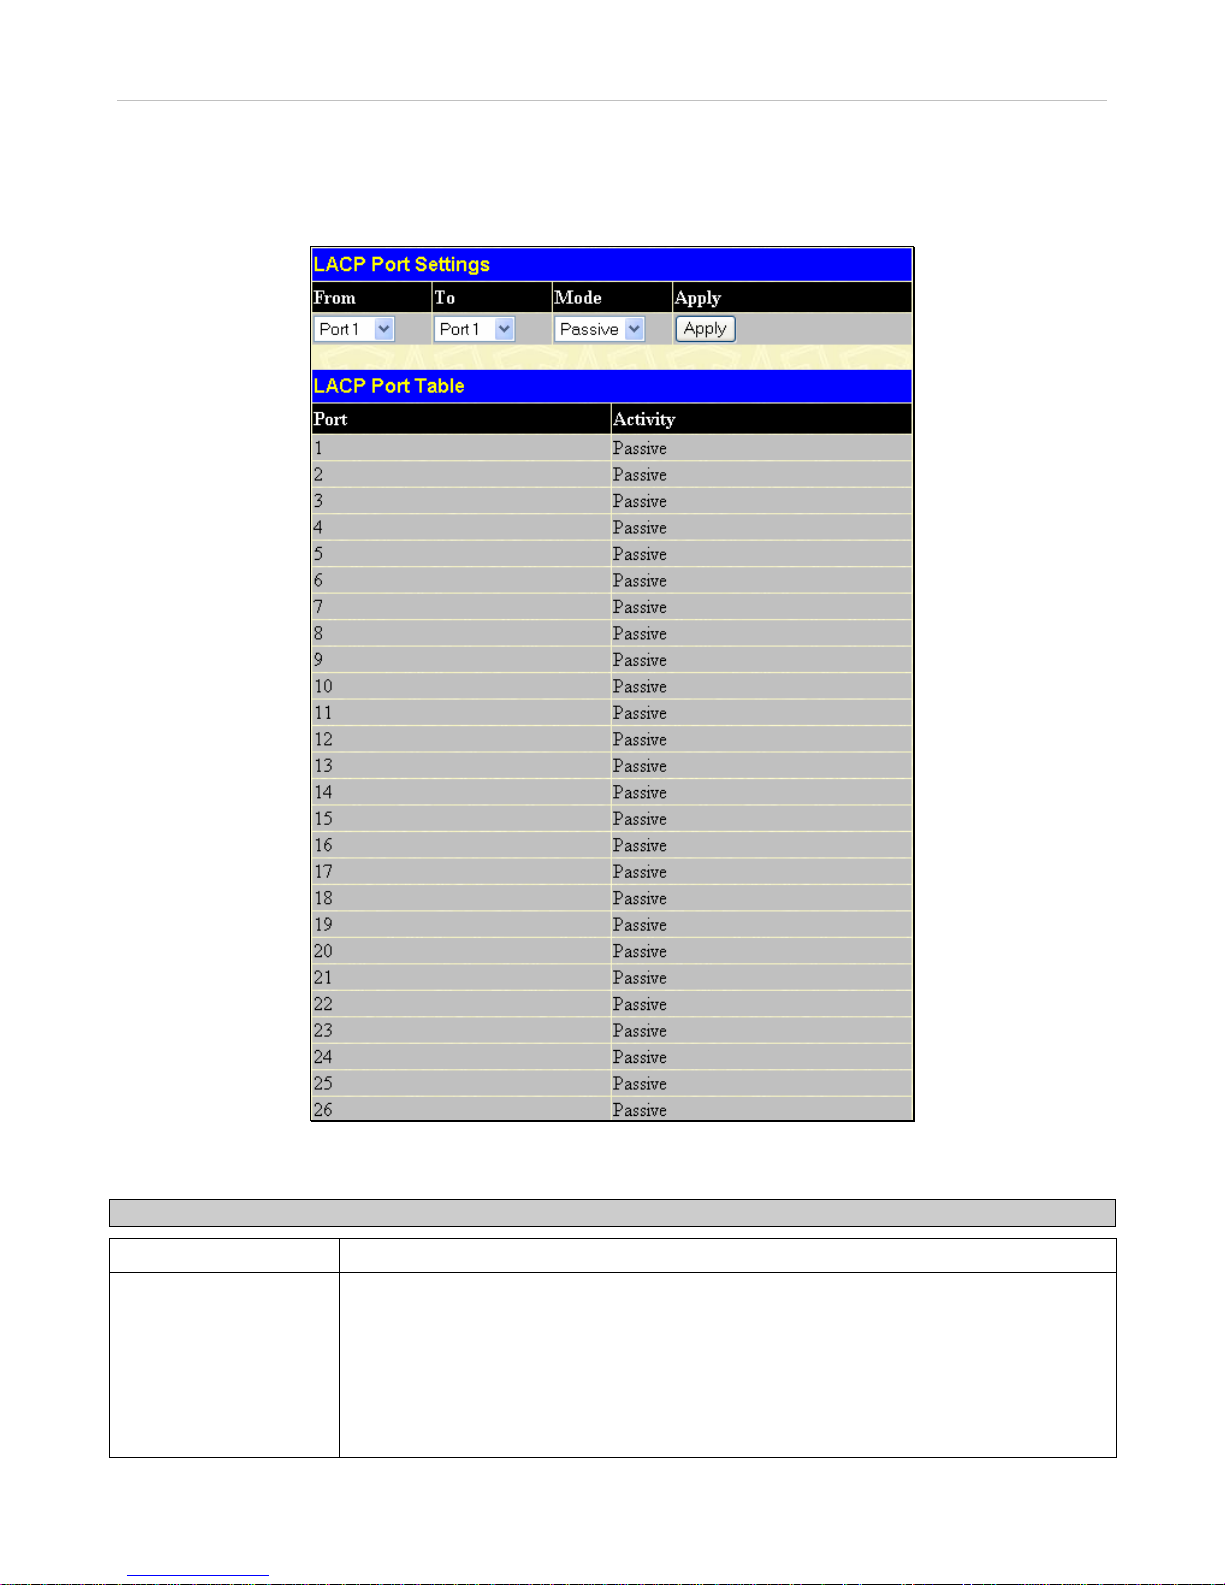
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
39
LACP Port Setting
The LACP Port Setting window is used in conjunction with the Link Aggregation window to create port trunk ing group s on th e
Switch. Using the following window, the user may set which ports will be active and passive in processing and sending LACP
control frames. To view this window, click Configuration > LACP Port Setting.
Figure 6- 11. LACP Port Settings window
The user may set the following parameters:
Parameter Description
From/To
A consecutive group of ports may be configured starting with the selected port.
Mode
Active - Active LACP ports are capable of processing and sending LACP control frames.
This allows LACP compliant devices to negotiate the aggregated link so the group may be
changed dynamically as needs require. In order to utilize the ability to change an
aggregated port group, that is, to add or subtract ports from the group, at least one of the
participating devices must designate LACP ports as active. Both devices must support
LACP.
Passive - LACP ports that are designated as passive cannot initially send LACP control
frames. In order to allow the linked port group to negotiate adjustments and make changes
Page 55
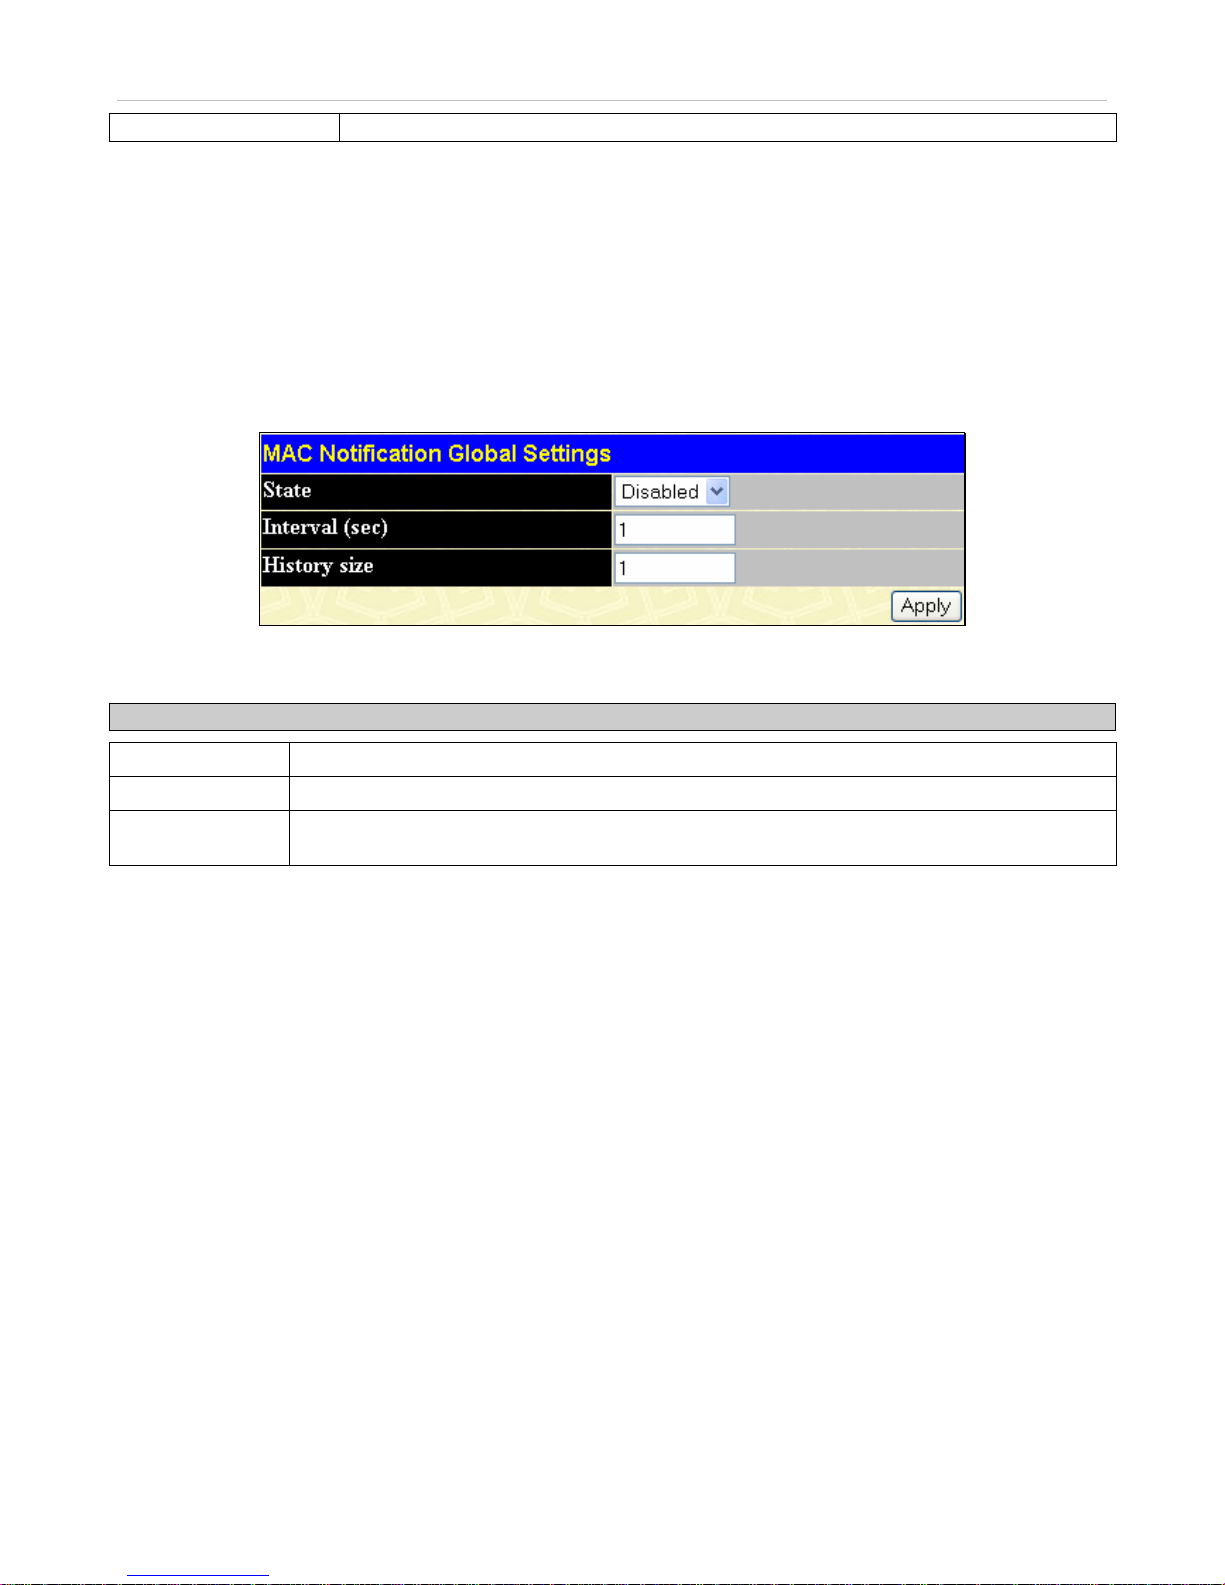
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
40
dynamically, one end of the connection must have "active" LACP ports (see above).
After setting the previous parameters, click Apply to allow your changes to be implemented. The LACP Port Table shows which
ports are active and/or passive.
MAC Notification
MAC Notification is used to monitor MAC addresses learned and entered into the forwarding database.
MAC Notification Global Settings
To globally set MAC notification on the Switch, open the following window b y opening Configuration > MAC Notification >
MAC Notification Global Settings:
Figure 6- 12. MAC Notification Global Settings window
The following parameters may be modified:
Parameter Description
State
Enable or disable MAC notification globally on the Switch
Interval (sec)
The time in seconds between notifications.
History size
The maximum number of entries listed in the history log used for notification. Up to 500 entries
can be specified.
Page 56
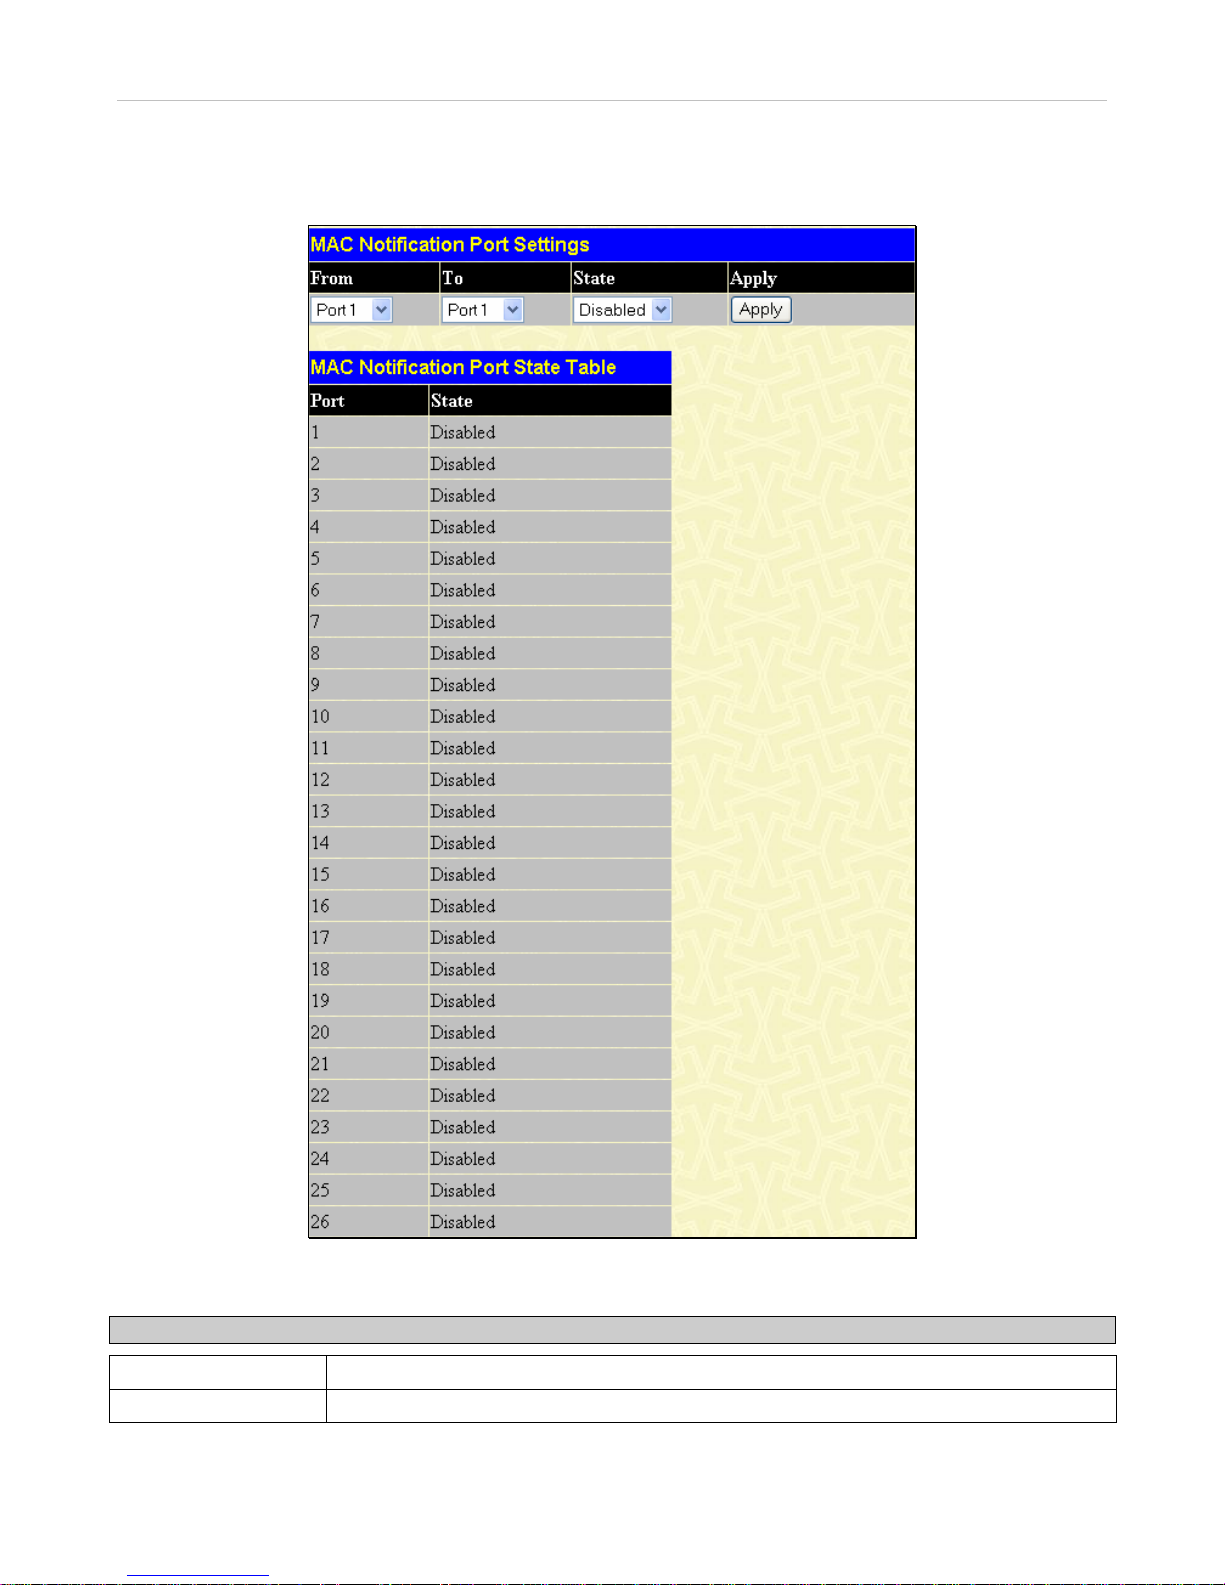
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
41
MAC Notification Port Settings
To change MAC notification settings for a port or group of ports on the Switch, click Configuration > MAC Notification >
MAC Notification Port Settings, which will display the following window:
Figure 6- 13. MAC Notification Port Settings window
The following parameters may be set:
Parameter Description
From…To
Select a port or group of ports to enable for MAC notification using the pull-down menus.
State
Enable MAC Notification for the ports selected using the pull-down menu.
Click Apply to implement changes made.
Page 57
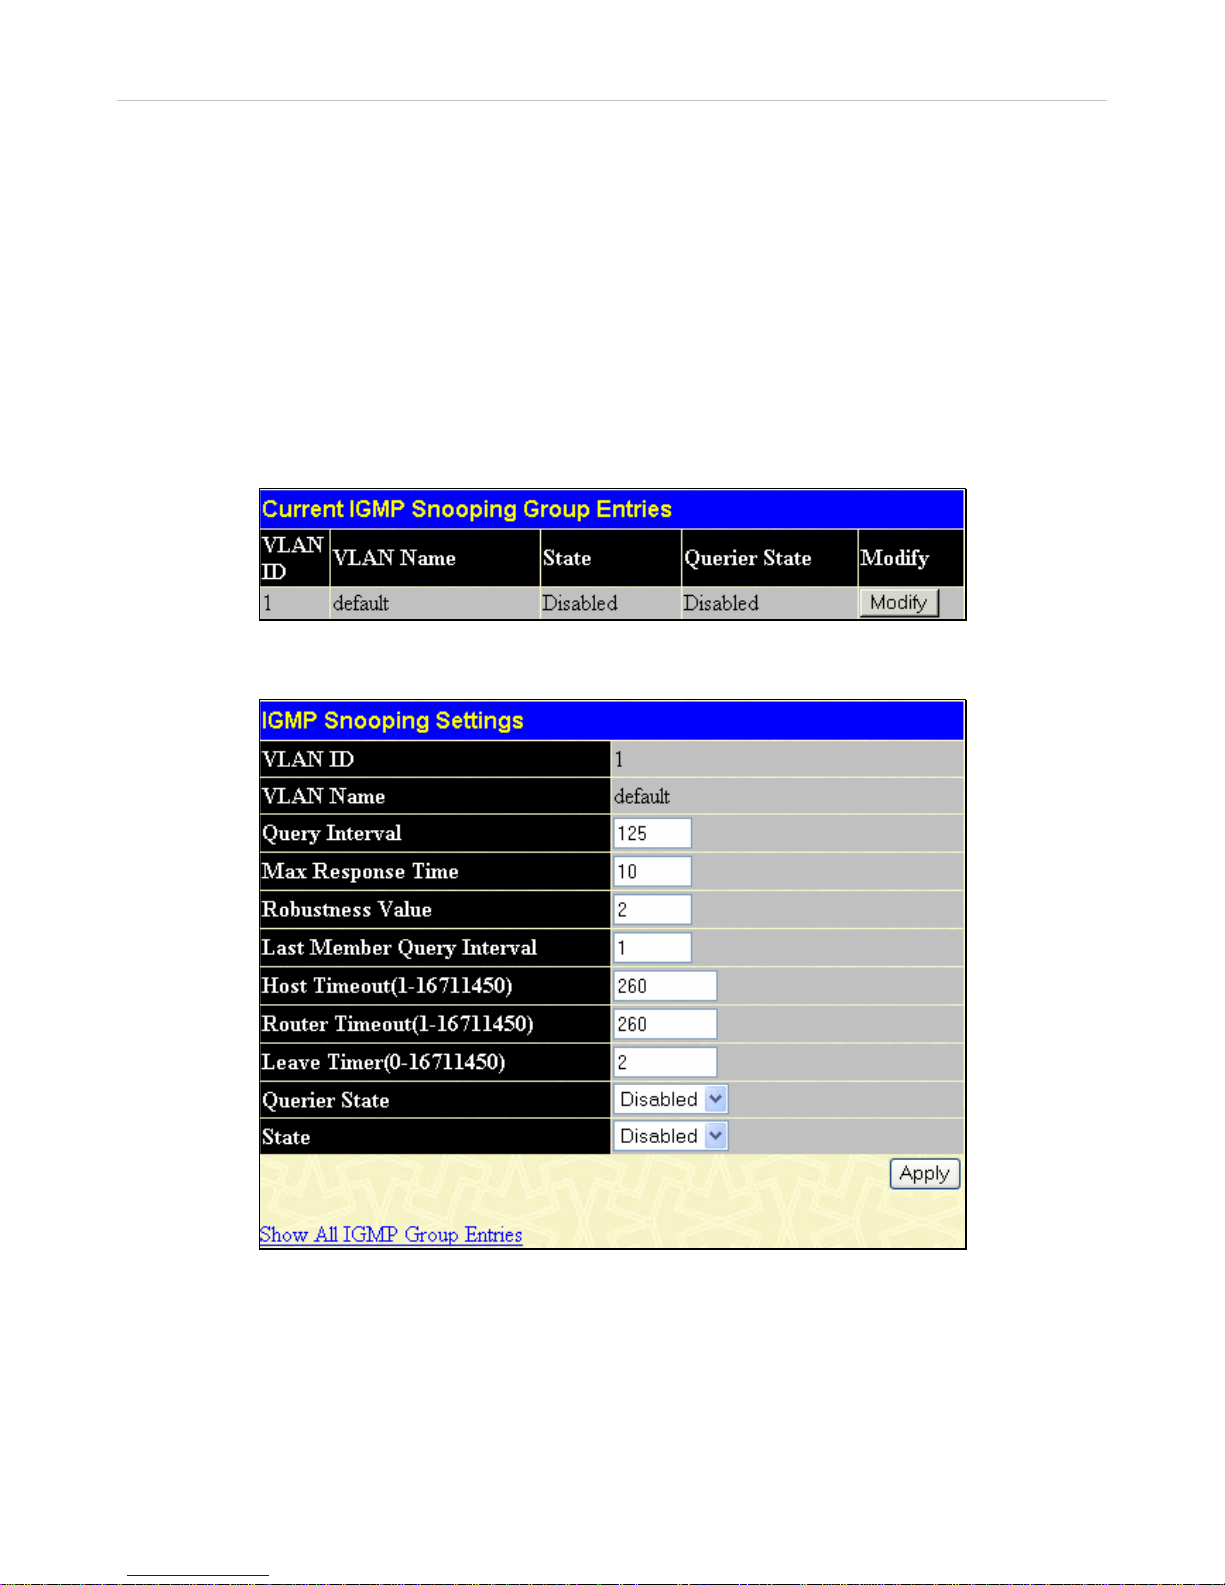
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
42
IGMP
Internet Group Management Protocol (IGMP) snooping allows the Switch to recogn ize IGMP queries and reports sent between
network stations or devices and an IGMP host. When enabled for IGMP snooping, the Switch can open or close a port to a
specific device based on IGMP messages passing through the Switch.
In order to use IGMP Snooping it must first be enabled for the entire Switch (see Advanced Settings). You may then fine-tune
the settings for each VLAN using the IGMP Snooping link in the Configuration folder. When enabled for IGMP snooping, the
Switch can open or close a port to a specific multicast group member based on IGMP messages sent from the device to the IGMP
host or vice versa. The Switch monitors IGMP messages and discontinues forwarding multicast packets when there are no longer
hosts requesting that they continue.
IGMP Snooping
Use the Current IGMP Snooping Group Entries window to view IGMP Snooping settings. To modify the settings, click the
Modify button of the VLAN ID you want to change. To view this window click, Configuration > IGMP > IGMP Snooping.
Figure 6- 14. Current IGMP Snooping Group Entries window
Clicking the Modify button will open the IGMP Snooping Settings window, shown below:
Figure 6- 15. IGMP Snooping Settings window
Page 58
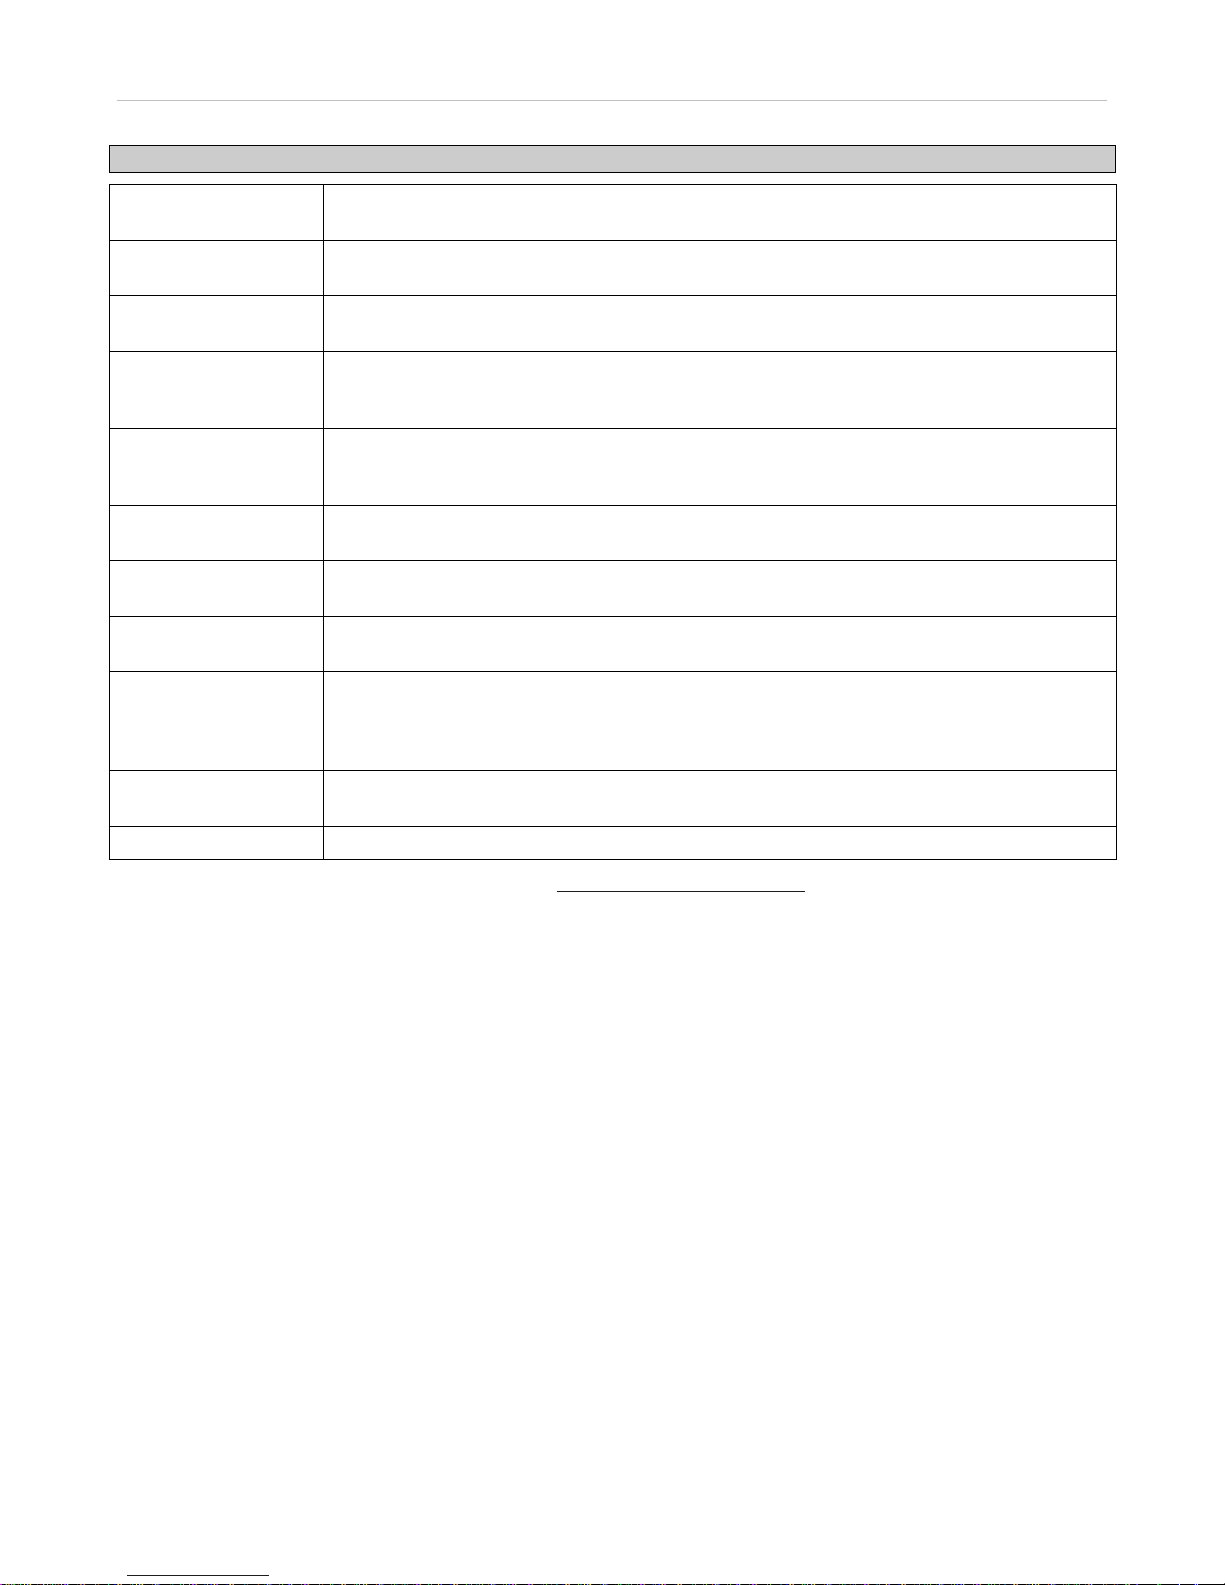
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
43
The following parameters may be viewed or modi fied:
Parameter Description
VLAN ID
This is the VLAN ID that, along with the VLAN Name, identifies the VLAN the user wishes to
modify the IGMP Snooping Settings for.
VLAN Name
This is the VLAN Name that, along with the VLAN ID, identifies the VLAN the user wishes to
modify the IGMP Snooping Settings for.
Query Interval
The Query Interval field is used to set the time (in seconds) between transmitting IGMP
queries. Entries between 1 and 65535 seconds are allowed. Default = 125.
Max Response Time
This determines the maximum amount of time in seconds allowed before sending an IGMP
response report. The Max Response Time field allows an entry between 1 and 25 (seconds).
Default = 10.
Robustness Variable
Adjust this variable according to expected packet loss. If packet loss on the VLAN is
expected to be high, the Robustness Variable should be increased to accommodate
increased packet loss. This entry field allows an entry of 1 to 255. Default = 2.
Last Member Query
Interval
This field specifies the maximum amount of time between group-specific query messages,
including those sent in response to leave group messages. Default = 1.
Host Timeout
This is the maximum amount of time in seconds allowed for a host to continue membership
in a multicast group without the Switch receiving a host membership report. Default = 260.
Router Timeout
This is the maximum amount of time in seconds a route is kept in the forwarding table
without receiving a membership report. Default = 260.
Leave Timer
This specifies the maximum amount of time in seconds between the Switch receiving a leave
group message from a host, and the Switch issuing a group membership query. If no
response to the membership query is received before the Leave Timer expires, the
(multicast) forwarding entry for that host is deleted.
Querier State
Choose Enabled to enable transmitting IGMP Query packets or Disabled to disable. The
default is Disabled.
State
Select Enabled to implement IGMP Snooping. This field is Disabled by default.
Click Apply to implement the new settings. Click the Show All IGMP Group Entries link to return to the Current IGMP
Snooping Group Entries window.
Page 59
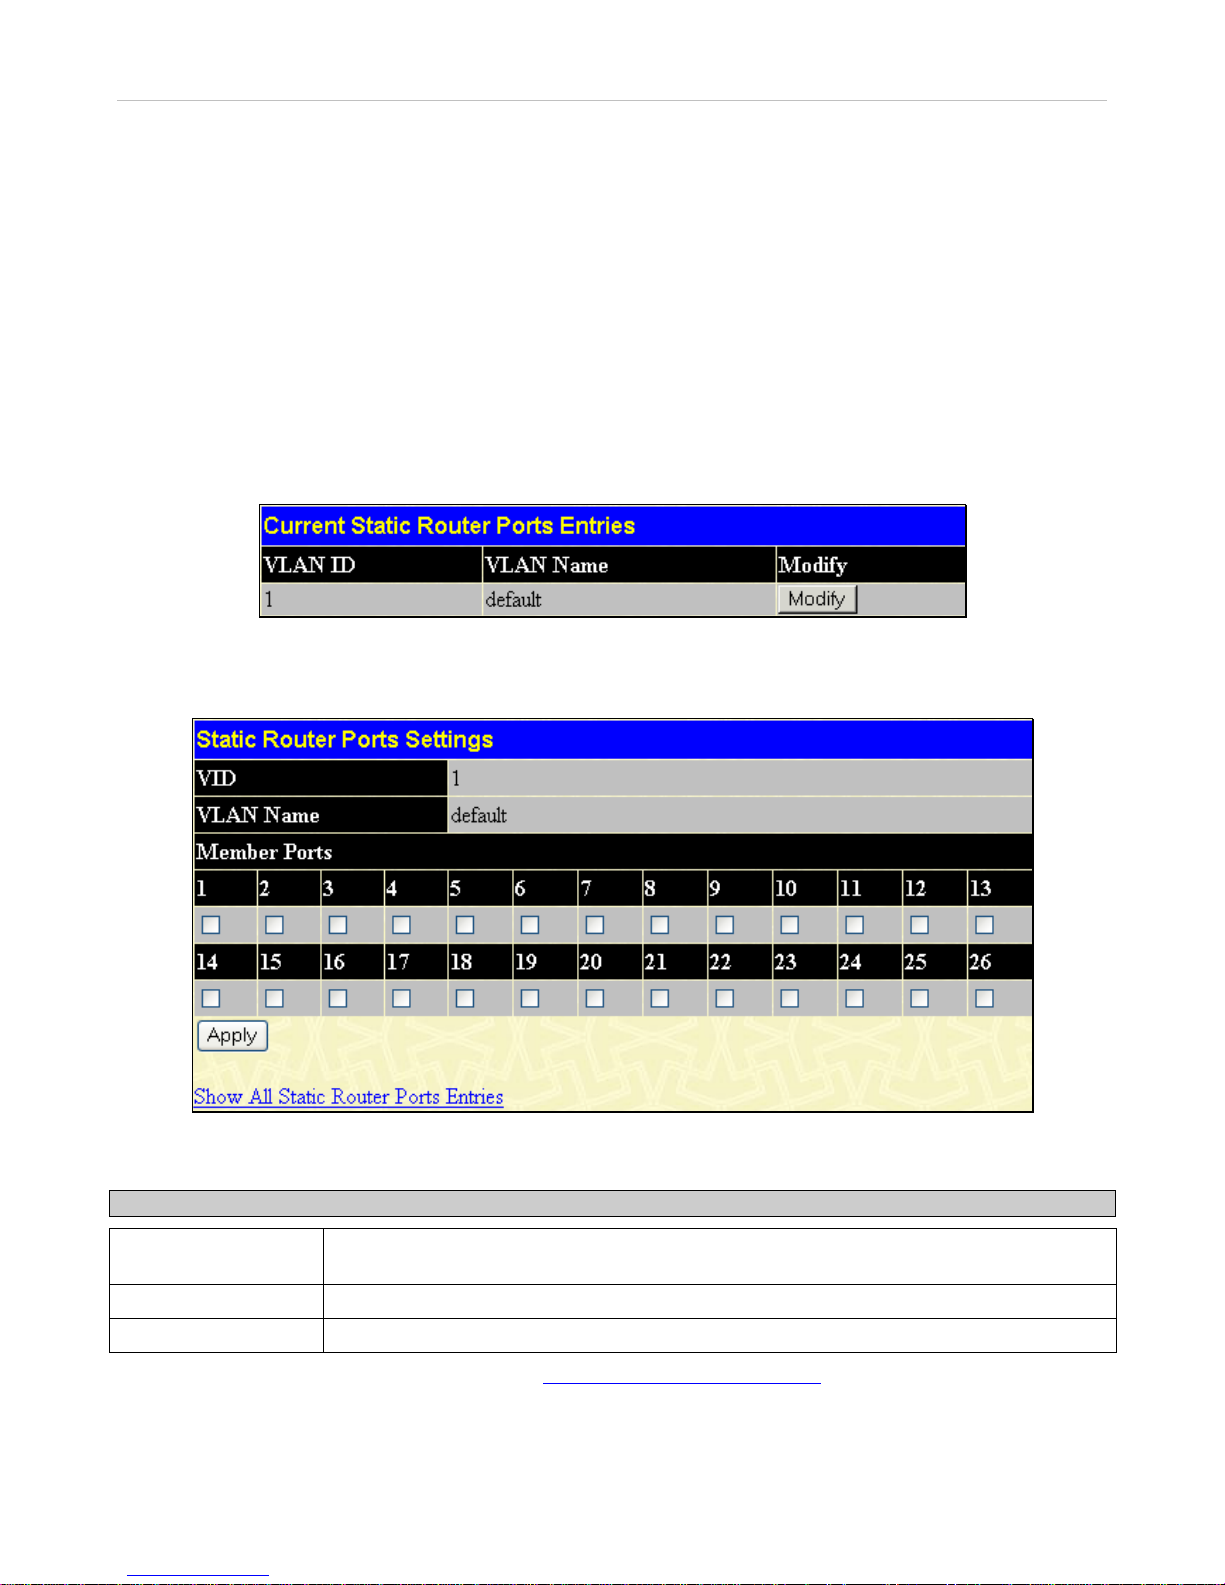
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
44
Static Router Ports Entry
A static router port is a port that has a multicast router attached to it. Generally, this router would have a connection to a WAN or
to the Internet. Establishing a router port will allow multicast packets coming from the router to be propagated through the
network, as well as allowing multicast messages (IGMP) coming from the network to be propagated to the router.
A router port has the following behavior:
• All IGMP Report packets will be forwarded to the router port.
• IGMP queries (from the router port) will be flooded to all ports.
• All UDP multicast packets will be forwarded to the router port. Because routers do not send IGMP reports or
implement IGMP snooping, a multicast router connected to the router port of a Layer 3 switch would not be able to
receive UDP data streams unless the UDP multicast packets were all forwarded to the router port.
A router port will be dynamically configured when IGMP query packets, RIPv2 multicast, DVMRP multicast or PIM-DM
multicast packets are detected flowing into a port.
To view this window click, Configuration > IGMP > Static Router Ports Entry.
Figure 6- 16. Current Static Router Ports Entries window
The Current Static Router Ports Entries window displays all of the current entries to the Switch's static router port table. To
modify an entry, click the Modify button. This will open the Static Router Ports Settings window, as shown below.
Figure 6- 17. Static Router Ports Settings window
The following parameters can be set:
Parameter Description
VID (VLAN ID)
This is the VLAN ID that, along with the VLAN Name, identifies the VLAN where the
multicast router is attached.
VLAN Name
This is the name of the VLAN where the multicast router is attached.
Member Ports
Ports on the Switch that will have a multicast router attached to them.
Click Apply to implement the new settings, Click the Show All Static Rou ter Port Entries link to return to the Current Static
Router Port Entries window.
Page 60
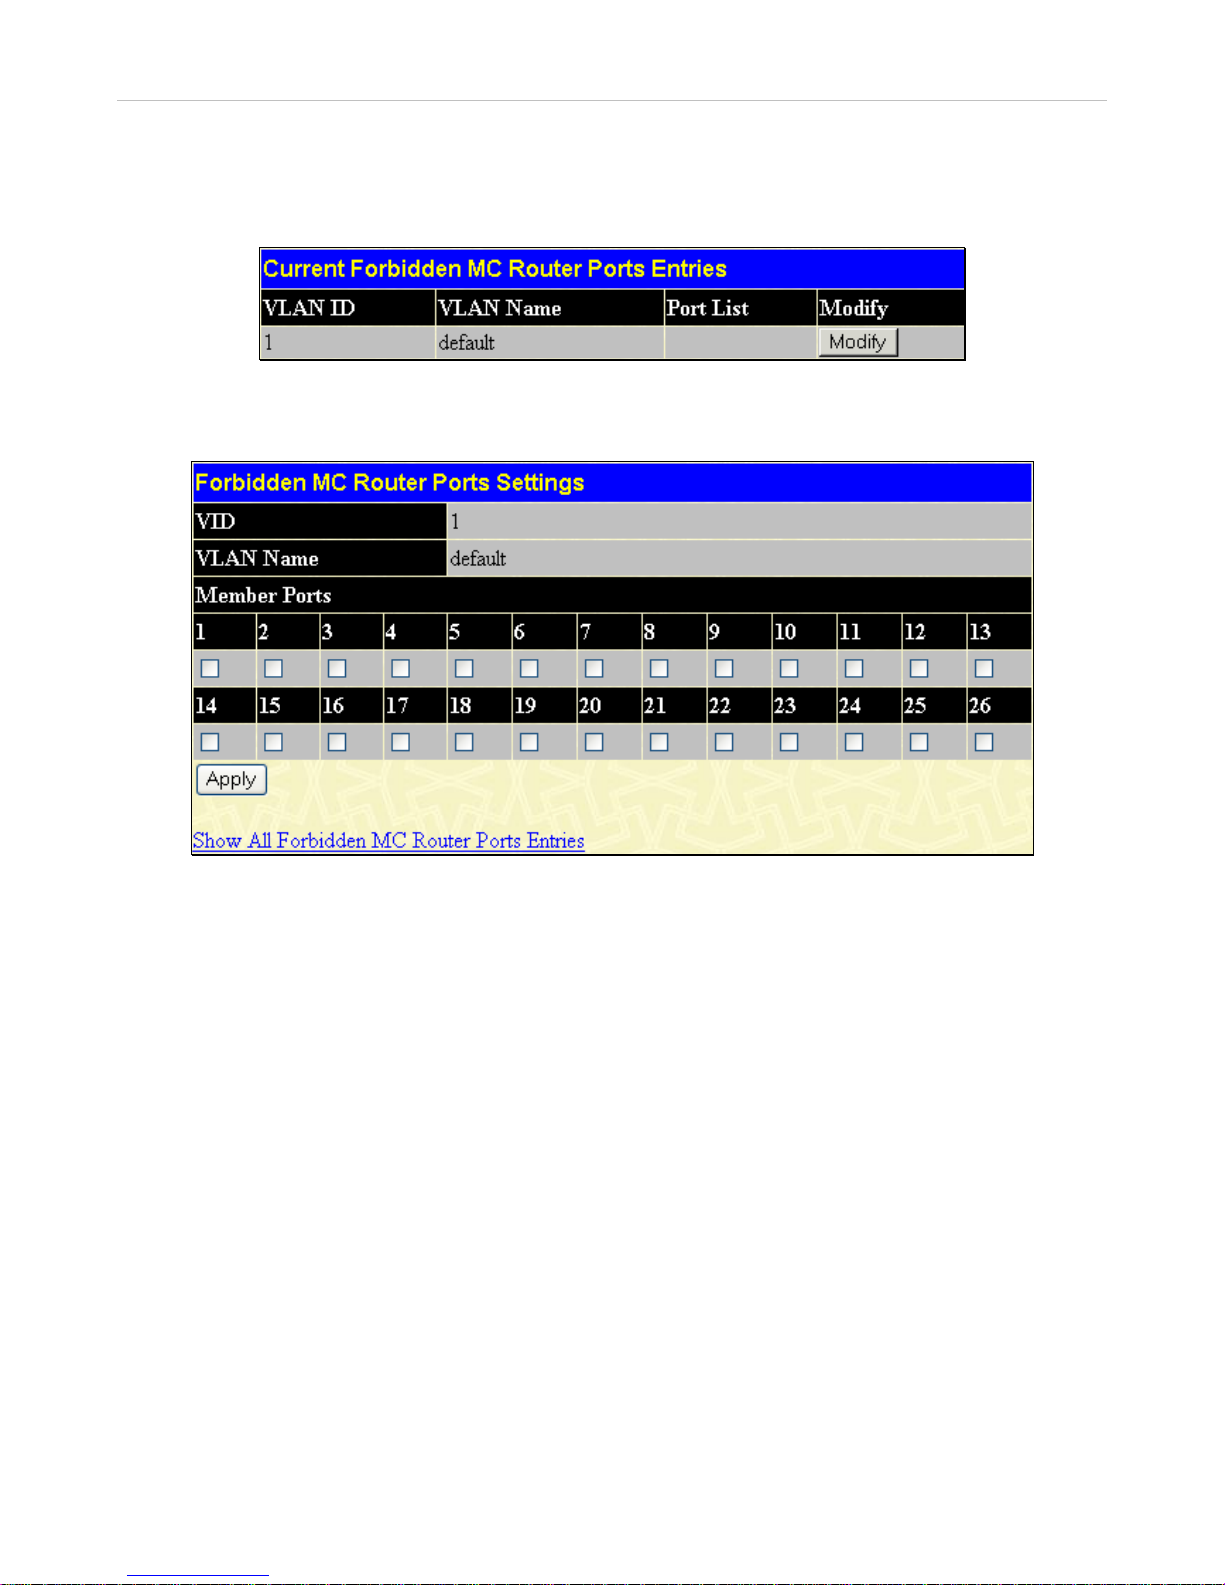
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
45
Forbidden Router Ports Entry
The Forbidden Router Ports Entry section will allow users to set a port or group of ports belonging to a VLAN as being forbidden
from receiving information from or being connected to multicast routers. To view the following window, click Configuration >
IGMP > Forbidden Router Ports Entry.
Figure 6- 18. Current Forbidden MC Router Ports Entries
To change the forbidden router ports settings for a listed VLAN, click its corresponding Modify button, which will display the
following configurable window.
Figure 6- 19. Forbidden MC Router Ports Settings
To add ports as forbidden router ports, click the corresponding check box of the port or ports, and click Apply. Properly set
forbidden ports will be displayed in the Current Forbidden MC Router Ports Entries window under the Port List heading.
Page 61
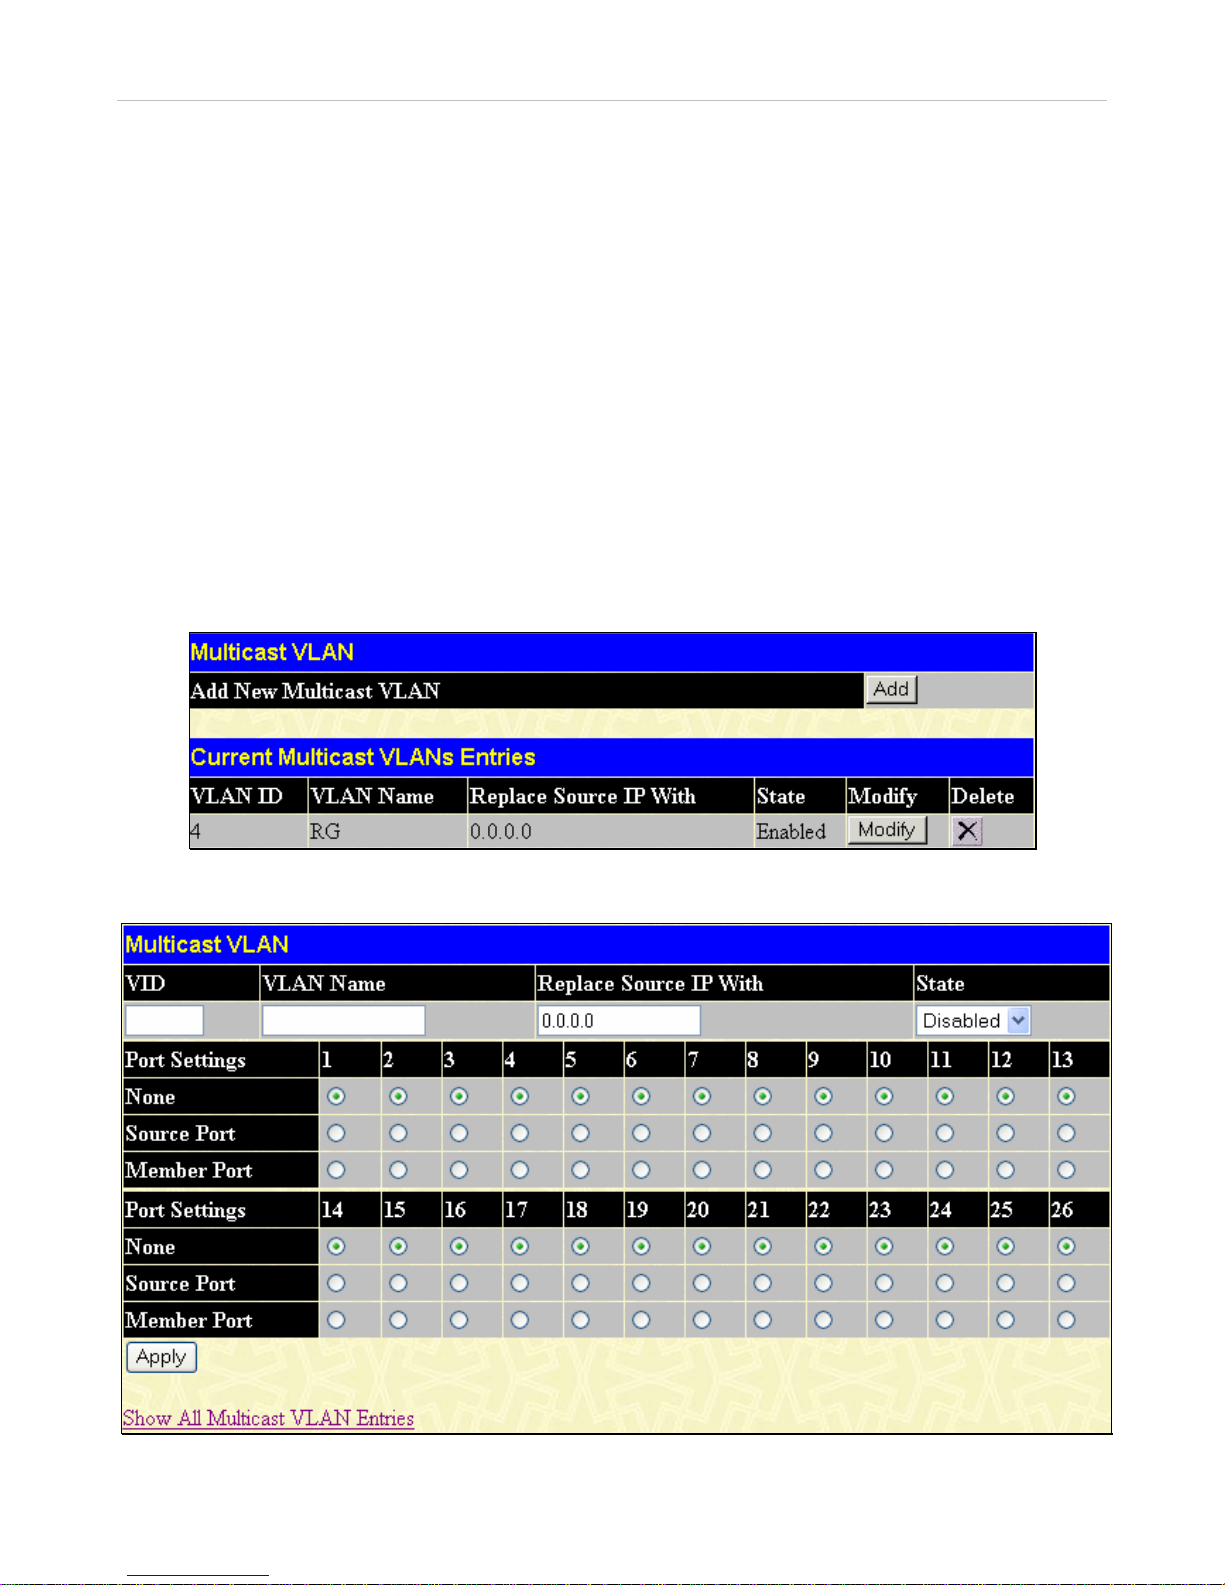
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
46
IGMP Multicast VLAN
Standard Internet Group Management Protocol (IGMP) snooping purposely limits multicast traffic so that only the interfaces
actively associating with the multicast are flooded. A layer 2 switch will snoop IGMP packet traffic between a multicast router
and host devices to learn and record the associated multicast groups and their member ports. A multicast forwarding table is
maintained for each multicast group. The table consists of entries that match the multicast group with ports used for the multicast.
A host will send an IGMP Join Group and Leave Group request when it wishes to receive or terminate a particular IP multicast.
The Switch also sends periodic queries to multicast routers for membership reports used to keep the multicast group tables up to
date.
IGMP snooping works well for enterprise or even campus level implementations using adequate and well-placed switching
capacity. However, IGMP snooping is problematic for service providers that wish to deploy subscriber-based multicast traffic in
an Ethernet switching environment when subscriber ports have their own unique VLAN; and because of the nature of the
communication between an IGMP snooping enabled switch and the multicast router. This creates a problem for sending multicasts
across separate VLANs.
The DES-3526 addresses this need by allowing the Switch to create a special network-wide shared VLANs used for multicasting.
This allows each port to be in separate VLANs while using the special VLAN for multicast streams. A subscriber may subscribe
(Join Group) or unsubscribe (Leave Group) to a multicast while the remaining subscribers are isolated from the multicast.
The Switch uses the special multicast VLAN to qualify MAC addresses in the Switch forwarding table as being members of the
multicast. It uses IGMP to modify the forwarding table, that is, to add or delete MAC addresses as it receives Join or Leave
requests from host devices.
To create IGMP Multicast VLANs for the Switch, click Configuration > IGMP > IGMP Multicast VLAN, which will display
the following window for the user to configure.
Figure 6- 20 Multicast VLAN and Current Multicast VLANs Entries Table
To create a new Multicast VLAN, click the Add button in the window above. The following window will be displayed.
Figure 6- 21 Multicast VLAN window - Add
Page 62
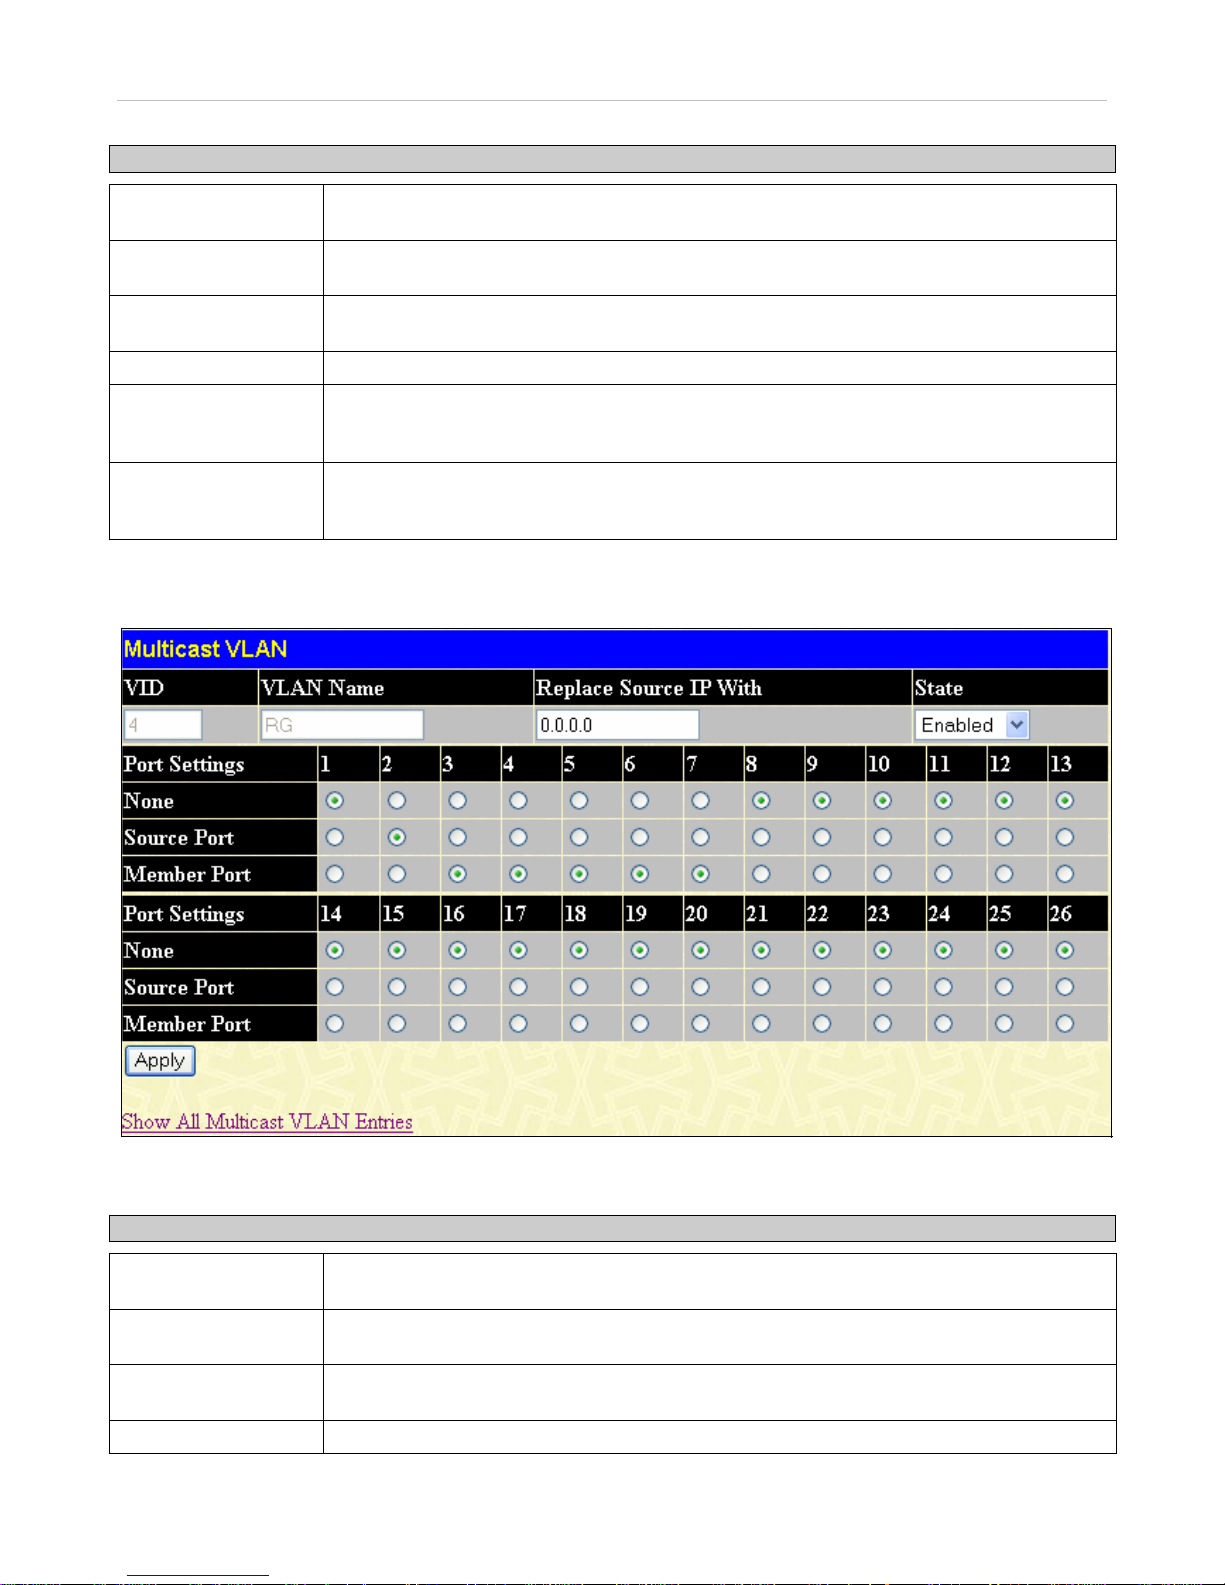
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
47
The following parameters can be set:
Parameter Description
VID
The VLAN ID of the multicast VLAN to be created. The user may choose a number between
1-4094 to identify this VLAN. Up to 3 multicast VLANs can be configured.
VLAN Name
The name of the multicast VLAN to be configured. Each multicast VLAN is given a name that
can be up to 32 characters. Up to 3 multicast VLANs can be configured.
Replace Source IP
With
Enter a source IP address that you want to replace.
State
The user may enable or disable this VLAN using the pull down menu here.
Source Port
A port on the Switch to be designated as the source port for multicast traffic. Multicast traffic
entering the switch will be forwarded from this port to member ports on the same VLAN.
Note that the Source port must be different from the member ports of the created VLAN.
Member Port
A port or range of member ports to add to the multicast VLAN. These ports will receive
multicast traffic from the source port. Remember, the source port cannot be the same as any
member port.
Click Apply to create the multicast VLAN.
To modify a previously created multicast VLAN, click the Modify button in the Current Multicast VLANs Entries Table,
which will display the following window for the user to configure.
Figure 6- 22 Multicast VLAN window - Modify
The following parameters can be set:
Parameter Description
VID
Displays the VLAN ID of the configured multicast VLAN. Up to 3 multicast VLANs can be
configured.
VLAN Name
The name of the configured multicast VLAN. Each multicast VLAN is given a name that can
be up to 32 characters. Up to 3 multicast VLANs can be configured.
Replace Source IP
With
Enter a source IP address that you want to replace in this field.
State
The user may enable or disable this VLAN using the pull down menu here.
Page 63
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
48
Source Port
A port on the Switch to be designated as the source port for multicast traffic. Multicast traffic
entering the switch will be forwarded from this port to member ports on the same VLAN.
Note that the Source port must be different from the member ports of the created VLAN.
Member Port
A port or range of member ports to add to the multicast VLAN. These ports will receive
multicast traffic from the source port. Remember, the source port cannot be the same as any
member port.
Click Apply to configure the multicast VLAN.
Note: Once a Multicast VLAN has been configured and enabled on the switch, other IGMP Snooping
settings will be overridden and the IGMP Snooping Multicast VLAN will take precedence.
Page 64
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
49
Spanning Tree
This Switch supports three versions of the Spanning Tree Protocol; 802.1d STP, 802.1w Rapid STP and 802.1s MSTP. 802.1d
STP will be familiar to most networking professionals. However, since 802.1w RSTP and 802.1s MSTP has been recently
introduced to D-Link managed Ethernet switches, a brief introduction to the technology is provided below followed by a
description of how to set up 802.1d STP, 802.1w RSTP and 80 2. 1s M STP.
802.1s MSTP
Multiple Spanning Tree Protocol, or MSTP, is a standard defined by the IEEE community that allows multiple VLANs to be
mapped to a single spanning tree instance, which will provide multiple pathways across the network. Therefore, these MSTP
configurations will balance the traffic load, preventing wide scale disruptions when a single spann ing tree instance fails. This will
allow for faster convergences of new topologies for the failed instance. Frames designated for these VLANs will be processed
quickly and completely throughout interconnected bridges utilizing any of the three spanning tree protocols (STP, RSTP or
MSTP).
This protocol will also tag BPDU packets so receiving devices can distinguish spanning tree instances, spanning tree regions and
the VLANs associated with them. An MSTI ID will classify these instances. MSTP will connect multiple spanning trees with a
Common and Internal Spanning Tree (CIST). The CIST will automatically determine each MSTP region, its maximum possible
extent and will appear as one virtual bridge that runs a single spanning tree. Consequentially, frames assigned to different VLANs
will follow different data routes within administratively established regions on the network, continuing to allow simple and full
processing of frames, regardless of administrative errors in defining VLANs and their respective spanning trees.
Each switch utilizing the MSTP on a network will have a single MSTP configuration that will have the following three attributes:
1. A configuration name defined by an alphanumeric string of up to 32 characters (defined in the STP Bridge Global
Settings window in the Configuration Name field).
2. A configuration revision number (named here as a Revision Level and found in the STP Bridge Global Settings window)
and;
3. A 4096-element table (defined here as a VID List in the MST Configuration Table window), which will associate each
of the possible 4096, VLANs supported by the Switch f or a given instance.
To utilize the MSTP function on the Switch, three steps need to be taken:
1. The Switch must be set to the MSTP setting (found in the STP Bridge Global Settings window in the STP Version field)
2. The correct spanning tree priority for the MSTP instance must be entered (defined here as a Priority in the MST
Configuration Table window when configuring an MSTI ID settings).
3. VLANs that will be shared must be added to the MSTP Instance ID (defined here as a VID List in the MST
Configuration Table window when configuring an MSTI ID settings).
802.1w Rapid Spanning Tree
The Switch implements three versions of the Spanning Tree Protocol, the Multiple Spanning Tree Protocol (MSTP) as defined by
the IEEE 802.1s, the Rapid Spanning Tree Protocol (RSTP) as defined by the IEEE 802.1w specification and a version compatible
with the IEEE 802.1d STP. RSTP can operate with legacy equipment implementing IEEE 802.1d, however the advantages of
using RSTP will be lost.
The IEEE 802.1w Rapid Spanning Tree Protocol (RSTP) evolved from the 802.1d STP standard. RSTP was developed in order to
overcome some limitations of STP that impede the function of some recent switching innovations, in particular, certain Layer 3
functions that are increasingly handled by Ethernet switches. The basic function and much of the terminology is the same as STP.
Most of the settings configured for STP are also used for RSTP. This section introduces some new Spanning Tree concepts and
illustrates the main differences between the two protocols.
Port Transition States
An essential difference between the three protocols is in the way ports transition to a forwarding state and in the way this
transition relates to the role of the port (forwarding or not forwarding) in the topology. MSTP and RSTP combine the transition
states disabled, blocking and listening used in 802.1d and creates a single state Discarding. In either case, ports do not forward
packets. In the STP port transition states disabled, blocking or listening or in the RSTP/MSTP port state discarding, there is no
functional difference, the port is not active in the network topology. Table 6-1 below compares how the three protocols differ
regarding the port state transition.
All three protocols calculate a stable topology in the same way. Every segment will have a single path to the root bridge. All
bridges listen for BPDU packets. However, BPDU packets are sent more frequently - with every Hello packet. BPDU packets are
sent even if a BPDU packet was not received. Therefore, each link between bridges is sensitive to the status of the link. Ultimately
this difference results in faster detection of failed links, and thus faster topology adjustment. A drawback of 802.1d is this absence
of immediate feedback from adjacent bridges.
Page 65
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
50
802.1d MSTP 802.1w RSTP 802.1d STP Forwarding Learning
Discarding Discarding Disabled No No
Discarding Discarding Blocking No No
Discarding Discarding Listening No No
Learning Learning Learning No Yes
Forwarding Forwarding Forwarding Yes Yes
Table 6- 1. Comparing Port States
RSTP is capable of a more rapid transition to a forwarding state - it no longer relies on timer configurations - RSTP compliant
bridges are sensitive to feedback from other RSTP compliant bridge links. Ports do not need to wait for the topology to stabilize
before transitioning to a forwarding state. In order to allow this rapid transition, the protocol introduces two new variables: the
edge port and the point-to-point (P2P) port.
Edge Port
The edge port is a configurable designation used for a port that is directly connected to a segment where a loop cannot be created.
An example would be a port connected directly to a single workstation. Ports that are designated as edge ports transition to a
forwarding state immediately without going through the listening and learning states. An edge port loses its status if it receives a
BPDU packet, immediately becoming a normal spanning tree port.
P2P Port
A P2P port is also capable of rapid transition. P2P ports may be used to connect to other bridges. Under RSTP/MSTP, all ports
operating in full-duplex mode are considered to be P2P ports, unless manually overridden through configuration.
802.1d/802.1w/802.1s Compatibility
MSTP or RSTP can interoperate with legacy equipment and is capable of automatically adjusting BPDU packets to 802.1d format
when necessary. However, any segment using 802.1d STP will not benefit from the rapid transition and rapid topology change
detection of MSTP or RSTP. The protocol also provides for a variable used for migration in the event that legacy equipment on a
segment is updated to use RSTP or MSTP.
The Spanning Tree Protocol (STP) operates on two levels:
1. On the switch level, the settings are globally implemented.
2. On the port level, the settings are implemented on a per user-defined group of ports basis.
Page 66
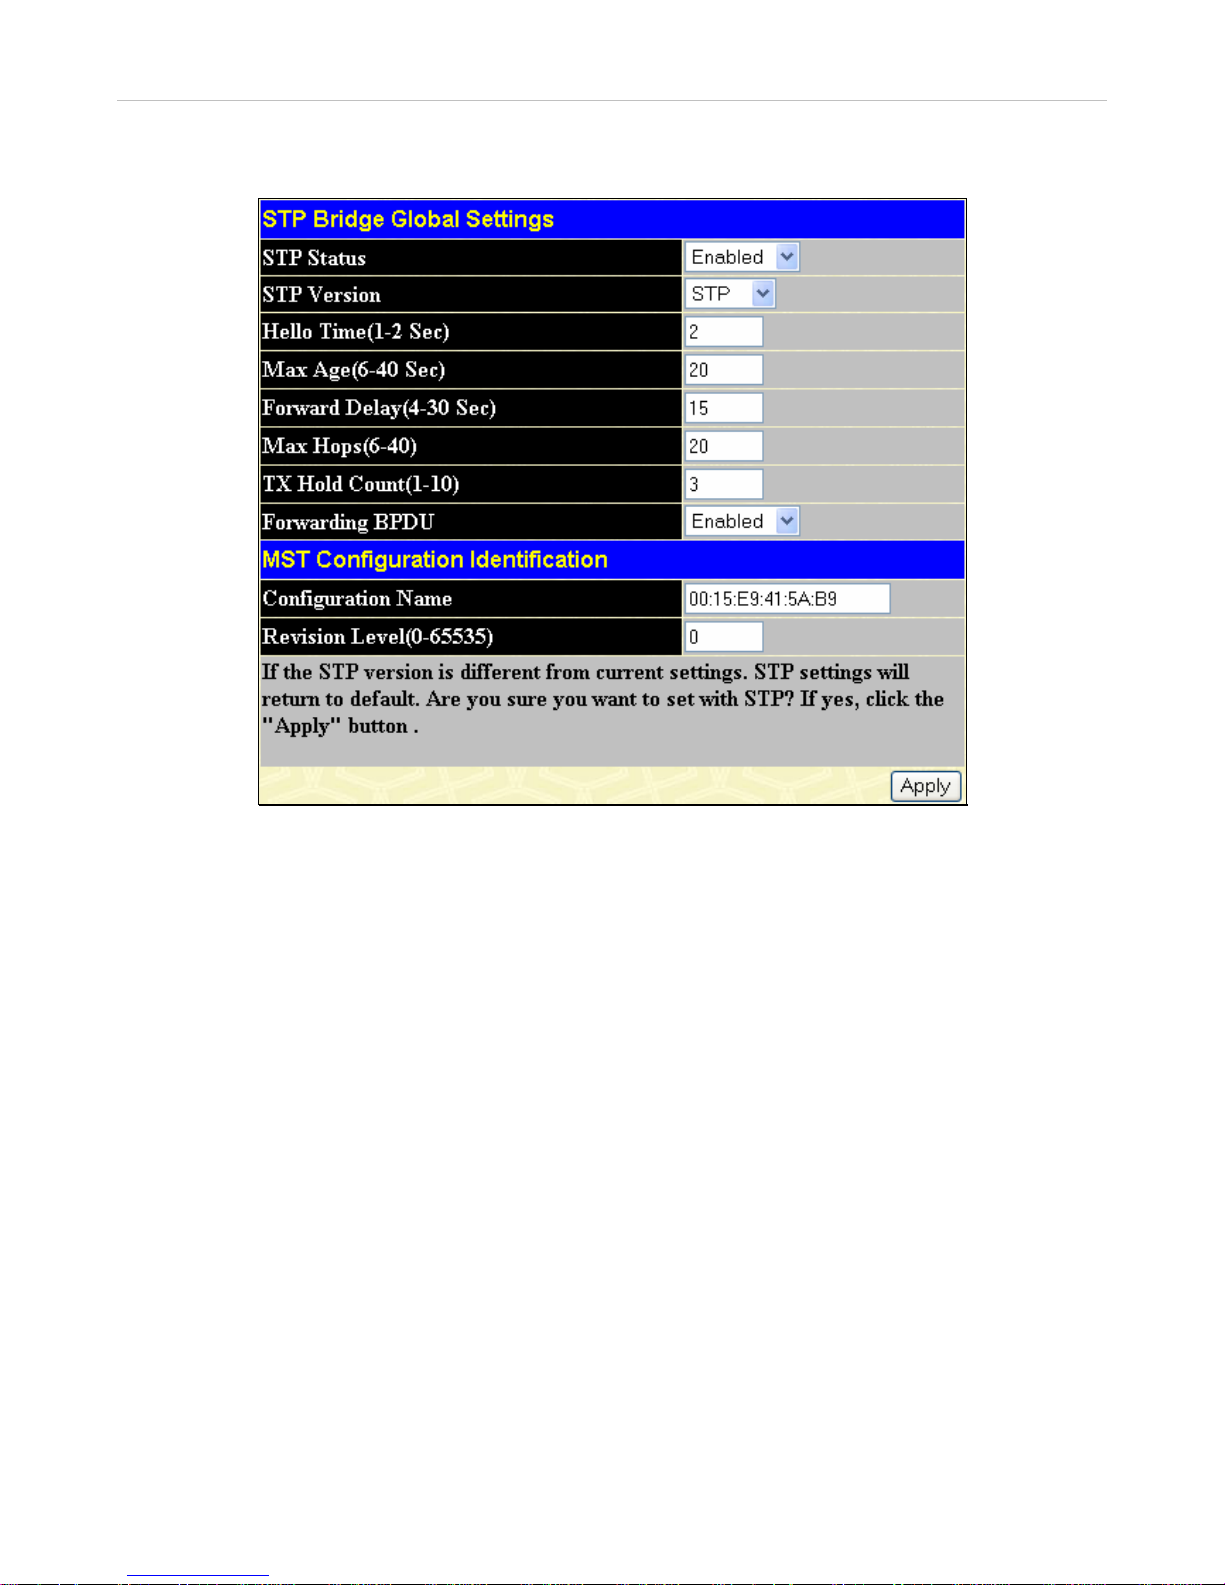
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
51
STP Bridge Global Settings
To view the STP Bridge Global Settings, click Configuration > Spanning Tree > STP Bridge Global Settings.
Figure 6- 23. STP Bridge Global Settings window - STP
Page 67
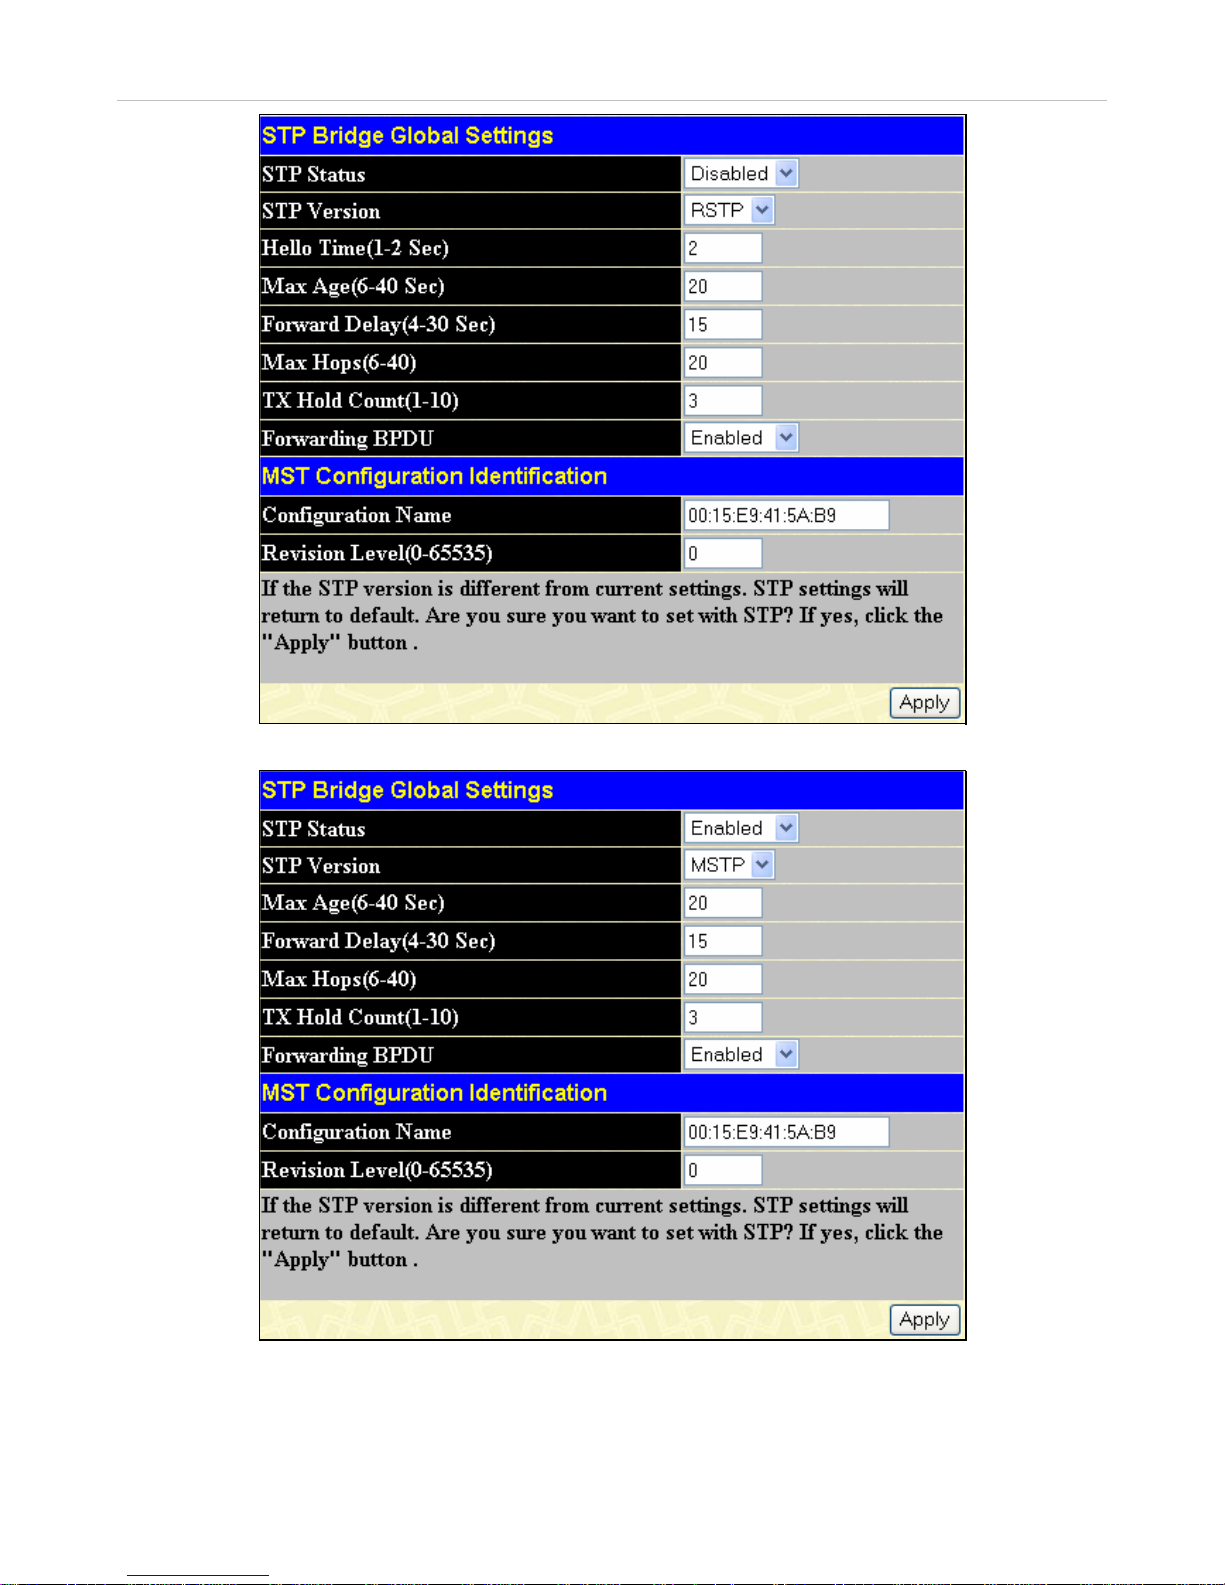
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
52
Figure 6- 24. STP Bridge Global Settings window - RSTP (default)
Figure 6- 25. STP Bridge Global Settings window - MSTP
Page 68
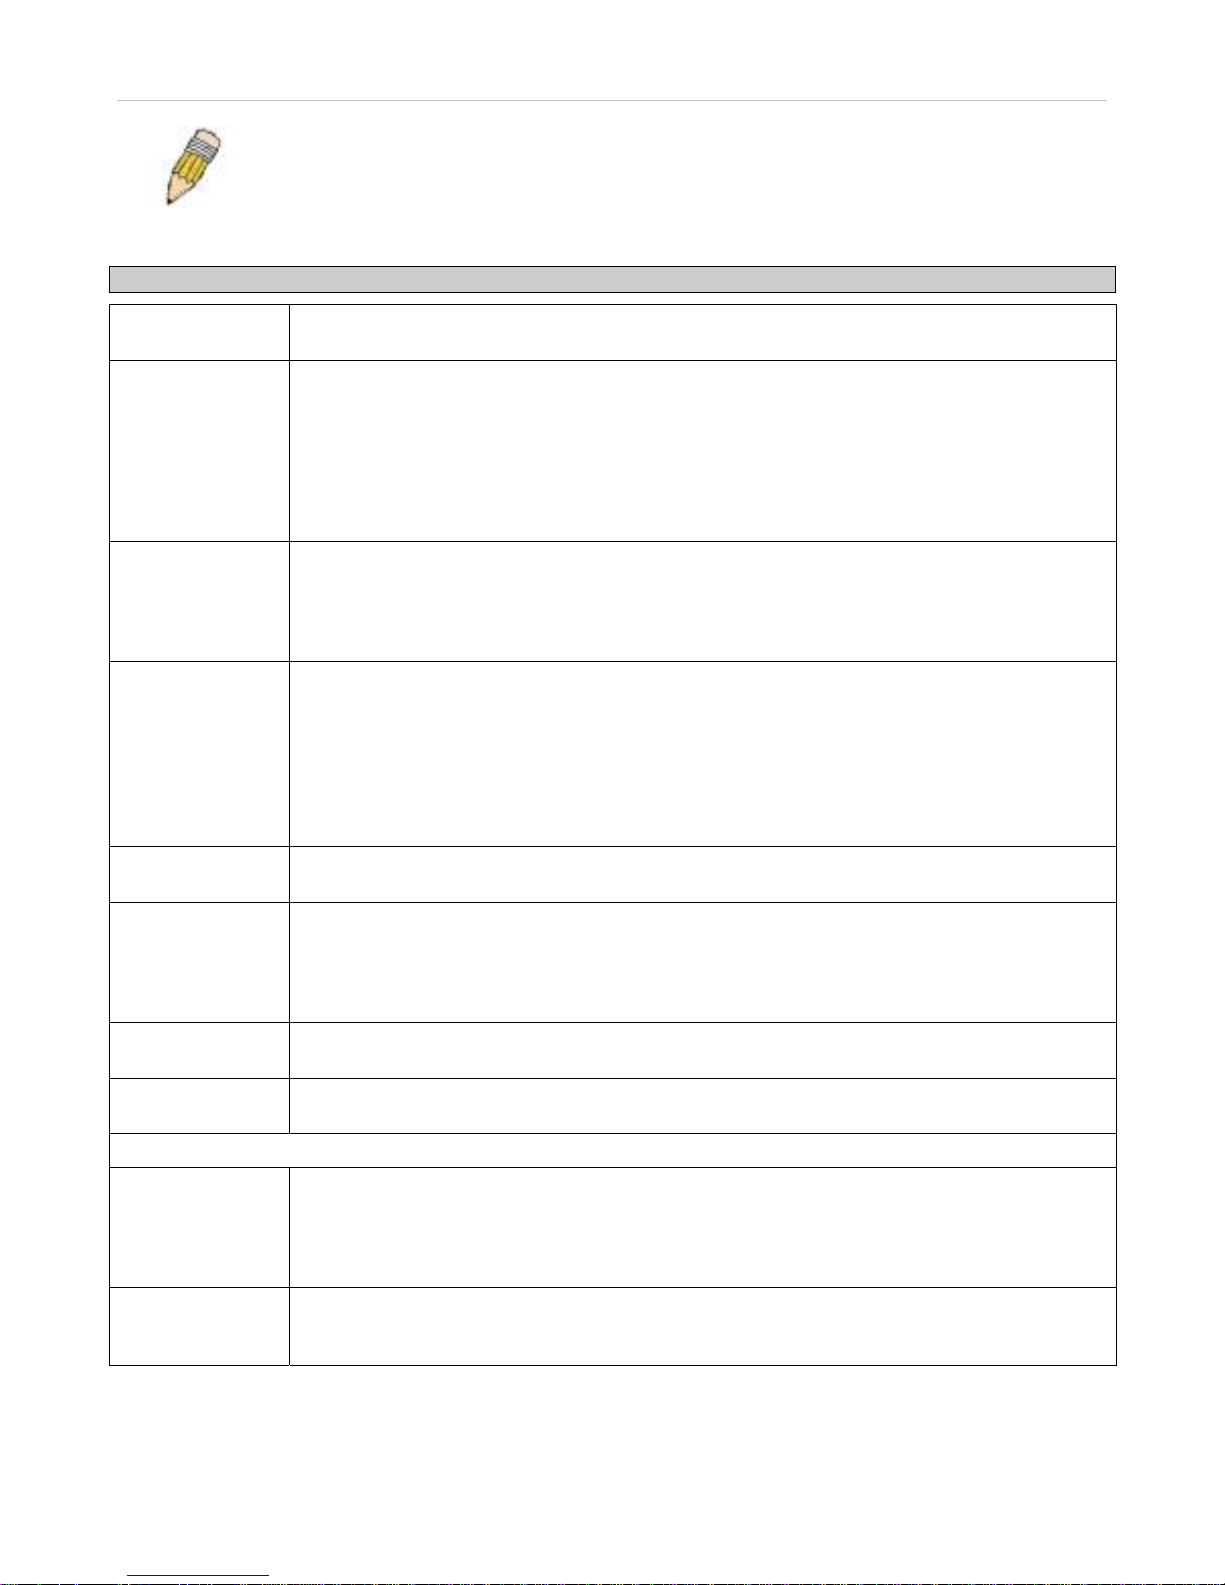
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
53
NOTE: The Hello Time cannot be longer than the Max. Age. Otherwise, a configuration error will
occur. Observe the following formulas when setting the above parameters:
Max. Age ≤ 2 x (Forward Delay - 1 second)
Max. Age ≥ 2 x (Hello Time + 1 second)
The following parameters can be set:
Parameter Description
STP Status
Use the pull-down menu to enable or disable STP globally on the Switch. The default is
Disabled.
STP Version
Use the pull-down menu to choose the desired version of STP to be implemented on the Switch.
There are three choices:
STP - Select this parameter to set the Spanning Tree Protocol (STP) globally on the switch.
RSTP - Select this parameter to set the Rapid Spanning Tree Protocol (RSTP) globally on the
Switch.
MSTP - Select this parameter to set the Multiple Spanning Tree Protocol (MSTP) globally on the
Switch.
Hello Time
The Hello Time can be set from 1 to 2 seconds. This is the interval between two transmissions of
BPDU packets sent by the Root Bridge to tell all other switches that it is indeed the Root Bridge.
This field will only appear here when STP or RSTP is selected for the STP Version. For MSTP,
the Hello Time must be set on a port per port basis. See the MST Port Settings section for further
details.
Max Age
The Max Age may be set to ensure that old information does not endlessly circulate through
redundant paths in the network, preventing the effective propagation of the new information. Set
by the Root Bridge, this value will aid in determining that the Switch has spanning tree
configuration values consistent with other devices on the bridged LAN. If the value ages out and
a BPDU has still not been received from the Root Bridge, the Switch will start sending its own
BPDU to all other switches for permission to become the Root Bridge. If it turns out that your
switch has the lowest Bridge Identifier, it will become the Root Bridge. The user may choose a
time between 6 and 40 seconds. The default value is 20.
Forward Delay
The Forward Delay can be from 4 to 30 seconds. Any port on the Switch spends this time in the
listening state while moving from the blocking state to the forwarding state.
Max Hops
Used to set the number of hops between devices in a spanning tree region before the BPDU
(bridge protocol data unit) packet sent by the Switch will be discarded. Each switch on the hop
count will reduce the hop count by one until the value reaches zero. The Switch will then discard
the BPDU packet and the information held for the port will age out. The user may set a hop count
from 1 to 20. The default is 20.
TX Hold Count
Used to set the maximum number of Hello packets transmitted per interval. The count can be
specified from 1 to 10. The default is 6.
Forwarding
BPDU
This field can be Enabled or Disabled. When Enabled, it allows the forwarding of STP BPDU
packets from other network devices. The default is Enabled.
MST Configuration Identification
Configuration
Name
Enter an alphanumeric string of up to 32 characters to uniquely identify the MSTP region on the
Switch. This Configuration Name, along with the Revision Level value will identify the MSTP
region configured on the Switch. If no name is entered, the default name will be the MAC
address of the device. This field is only valid when MSTP is the version of STP globally set on
the Switch.
Revision Level
Enter a number between 0 and 65535 to identify the MSTP region. This value, along with the
name will identify the MSTP region configured on the Switch. The default setting is 0. This field is
only valid when MSTP is the version of STP globally set on the Switch.
Click Apply to implement changes made.
Page 69
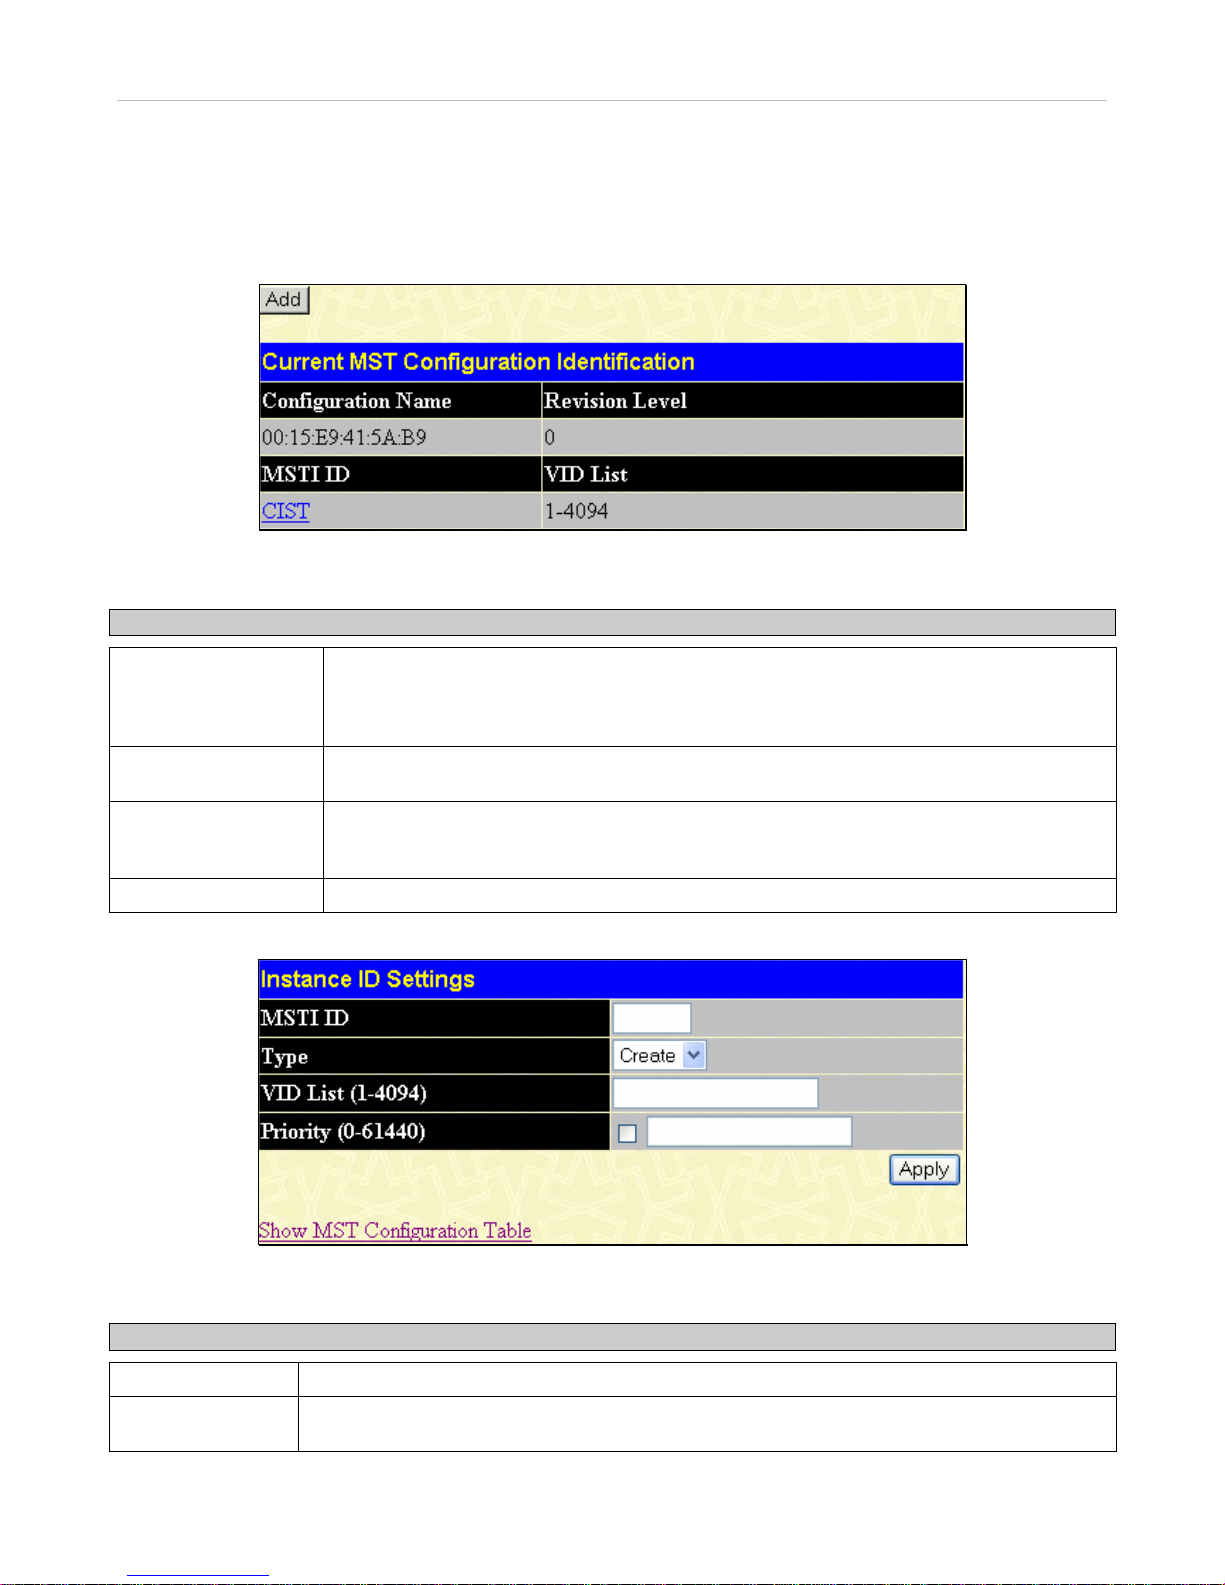
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
54
MST Configuration Table
The following screens in the MST Configuration Table window allow the user to configure a MSTI instance on the Switch.
These settings will uniquely identify a multiple spanning tree instance set on the Switch. The Switch initially possesses one CIST
or Common Internal Spanning Tree of which the user may modify the parameters for but cannot change the MSTI ID for, and
cannot be deleted. To view the Current MST Configuration Identification window, click Configuration > Spanning Tree >
MST Configuration Table:
Figure 6- 26. Current MST Configuration Identification window
The window above contains the following information:
Parameter Description
Configuration Name
A previously configured name set on the Switch to uniquely identify the MSTI (Multiple
Spanning Tree Instance). If a configuration name is not set, this field will show the MAC
address to the device running MSTP. This field can be set in the STP Bridge Global Settings
window.
Revision Level
This value, along with the Configuration Name will identify the MSTP region configured on
the Switch. This field can also be set in the STP Bridge Global Settings window.
MSTI ID
This field shows the MSTI IDs currently set on the Switch. This field will always have the
CIST MSTI, which may be configured but not deleted. Clicking the hyperlinked name will
open a new window for configuring parameters associated with that particular MSTI.
VID List
This field displays the VLAN IDs associated with the specific MSTI.
Clicking the Add button will reveal the following window to configure:
Figure 6- 27. Instance ID Settings window – Add
The user may configure the following parameters to create a MSTI in the Switch.
Parameter Description
MSTI ID
Enter a number between 1 and 4 to set a new MSTI on the Switch.
Type
Create is selected to create a new MSTI. No other choices are available for this field when
creating a new MSTI.
Page 70
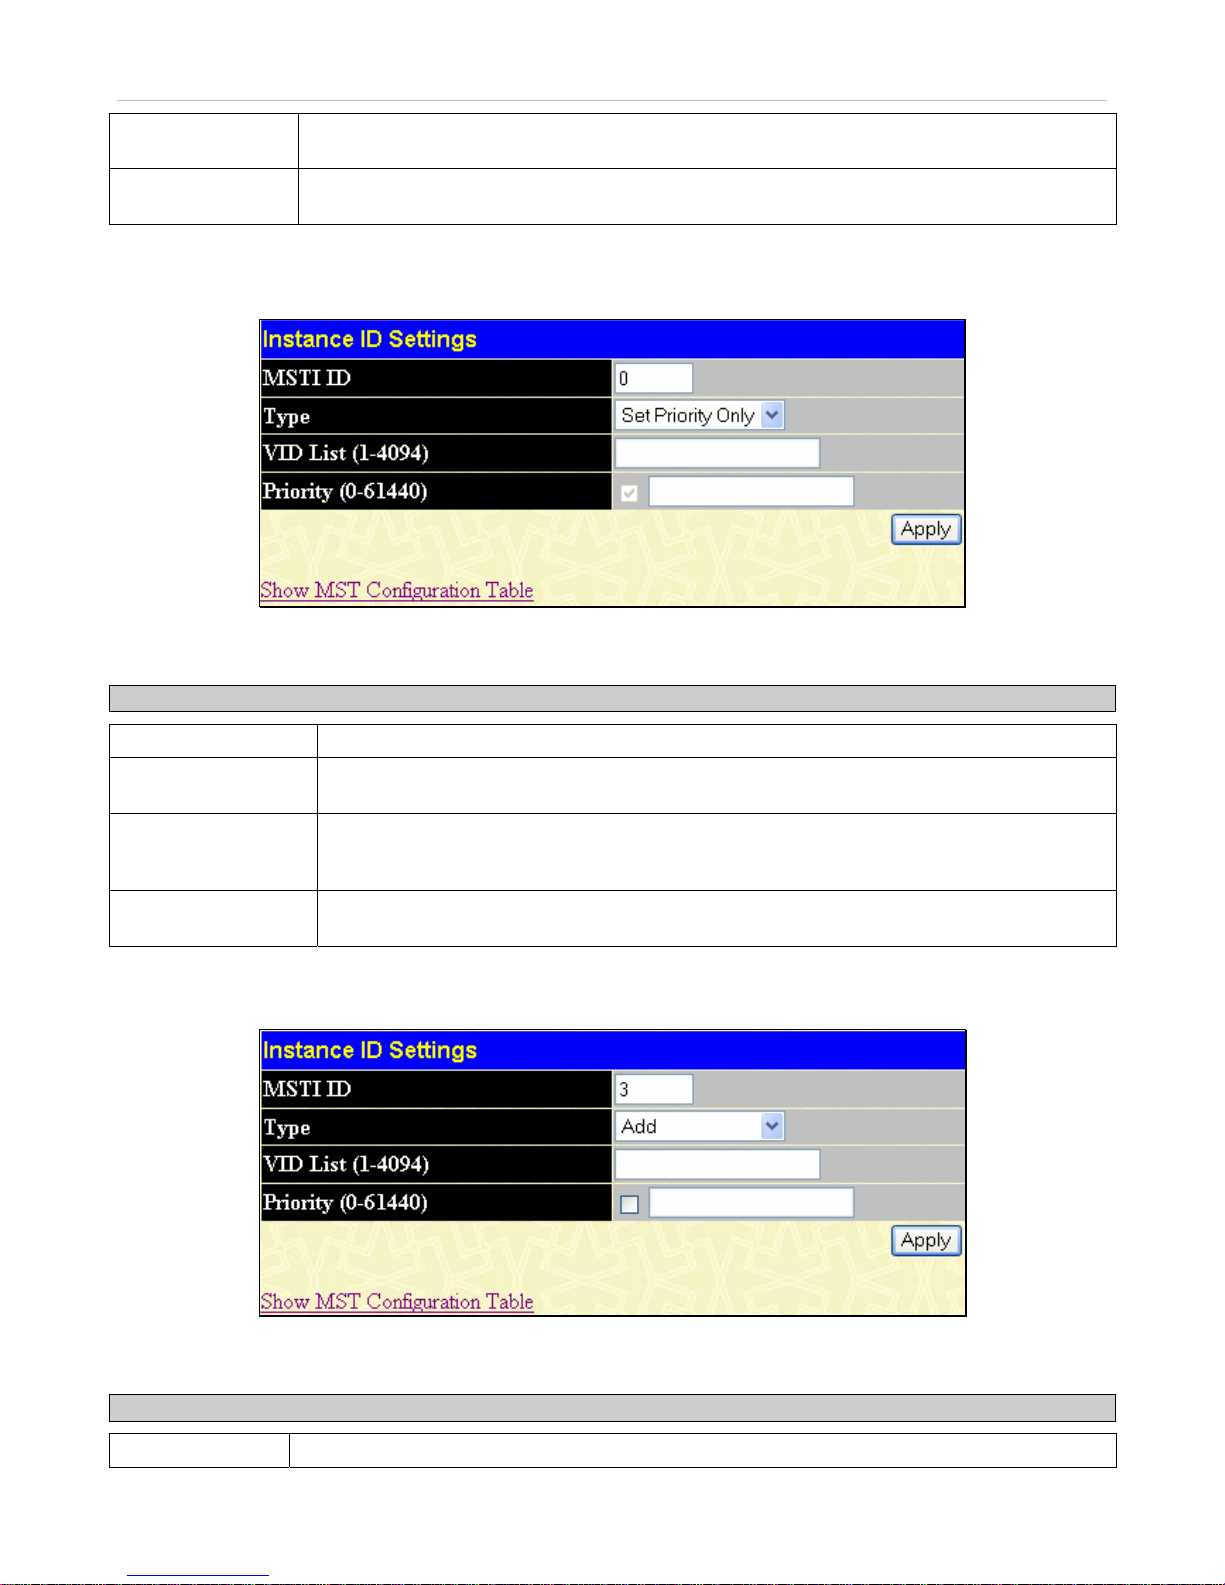
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
55
VID List (1-4094)
This field is used to specify the VID range from configured VLANs set on the Switch. Supported
VIDs on the Switch range from ID number 1 to 4094.
Priority (0-61440)
Select a value between 0 and 61440 to specify the priority for a specified MSTI for forwarding
packets. The lower the value, the higher the priority. This entry must be divisible by 4094.
Click Apply to implement changes made.
To configure the settings for the CIST, click on its hyperlinked name in the Current MST Configuration Identification window,
which will reveal the following window to configure:
Figure 6- 28. Instance ID Settings window - CIST modify
The user may configure the following parameters to configure the CIST on the Switch.
Parameter Description
MSTI ID
The MSTI ID of the CIST is 0 and cannot be altered.
Type
The type of configuration about to be processed. This window is used to set the priority for
the CIST only. All other parameters are permanently set and therefore unchangeable.
VID List (1-4094)
This field is used to specify the VID range from configured VLANs set on the Switch.
Supported VIDs on the Switch range from ID number 1 to 4094. This field is inoperable when
configuring the CIST.
Priority (0-61440)
Select a value between 0 and 61440 to specify the priority for a specified MSTI for forwarding
packets. The lower the value, the higher the priority. This entry must be divisible by 4094.
Click Apply to implement changes made.
To configure the parameters for a previously set MSTI, click on its hyperlinked MSTI ID number, which will reveal the following
window for configuration.
Figure 6- 29. Instance ID Settings window – modify
The user may configure the following parameters for a MSTI on the Switch.
Parameter Description
MSTI ID
Displays the MSTI ID previously set by the user.
Page 71
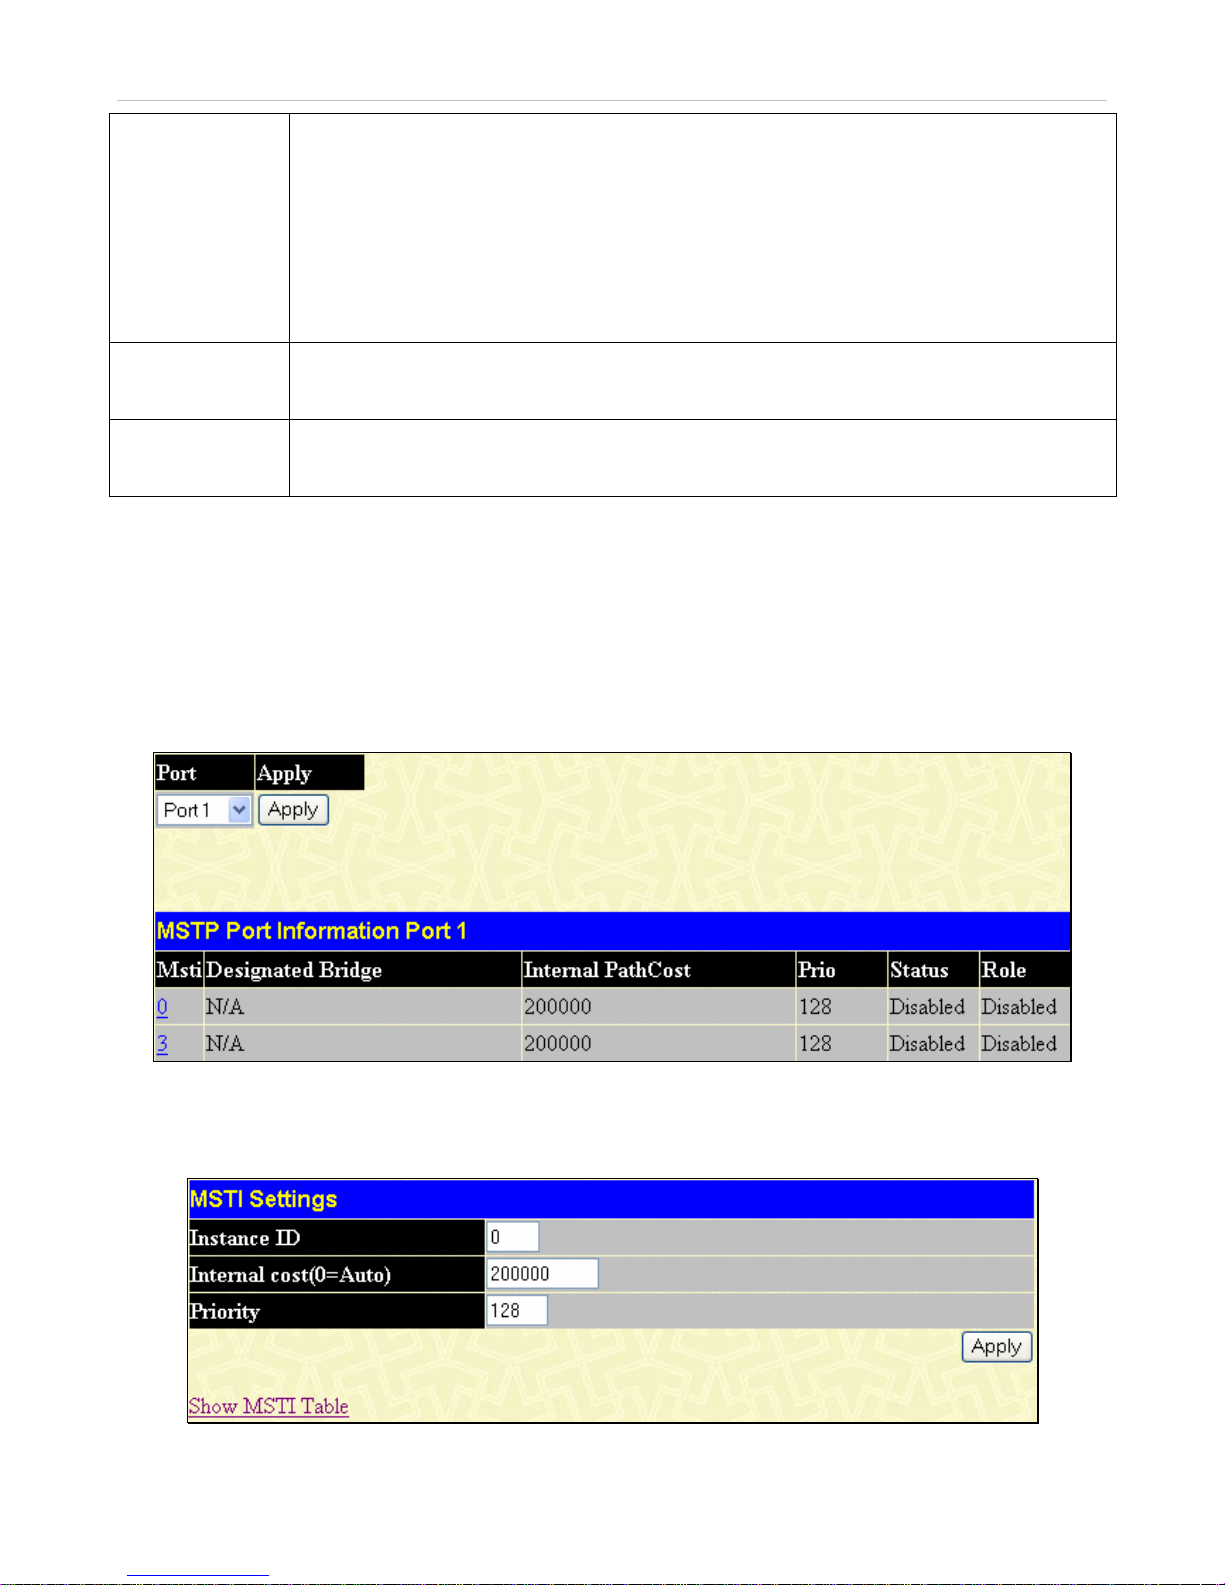
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
56
Type
This field allows the user to choose a desired method for altering the MSTI settings. The user
has four choices.
• Add - Select this parameter to add VIDs to the MSTI ID, in conjunction with the VID List
parameter.
• Remove - Select this parameter to remove VIDs from the MSTI ID, in conjunction with
the VID List parameter.
• Delete - Select this parameter to delete this MSTI ID.
• Set Priority Only - Select this parameter to set the priority for the MSTI ID. This field is
used in conjunction with the Priority field.
VID List (1-4094)
This field is used to specify the VID range from configured VLANs set on the Switch that the user
wishes to add to this MSTI ID. Supported VIDs on the Switch range from ID number 1 to 4094.
This parameter can only be utilized if the Type chosen is Add or Remove.
Priority (0-61440)
Select a value between 0 and 61440 to specify the priority for a specified MSTI for forwarding
packets. The lower the value, the higher the priority. This entry must be divisible by 4094 and
can only be utilized if the Type chosen is Set Priority Only.
Click Apply to implement changes made.
MSTI Settings
This window displays the current MSTI configuration settings and can be used to update the port configuration for an MSTI ID. If
a loop occurs, the MSTP function will use the port priority to select an interface to put into the forwarding state. Set a higher
priority value for interfaces to be selected for forwarding first. In instances where the priority value is identical, the MSTP
function will implement the lowest MAC address into the forwarding state and other interfaces will be b locked. Remember that
lower priority values mean higher priorities for forwarding packets.
To view the following window, click Configuration > Spanning Tree > MSTI Settings:
Figure 6- 30. MSTI Port Information window
To view the MSTI settings for a particular port, select the Port number, located in the top left hand corner of the screen and click
Apply. To modify the settings for a particular MSTI Instance, click on its hyperlinked MSTI ID, which will reveal the following
window.
Figure 6- 31. MSTI Settings window
Page 72
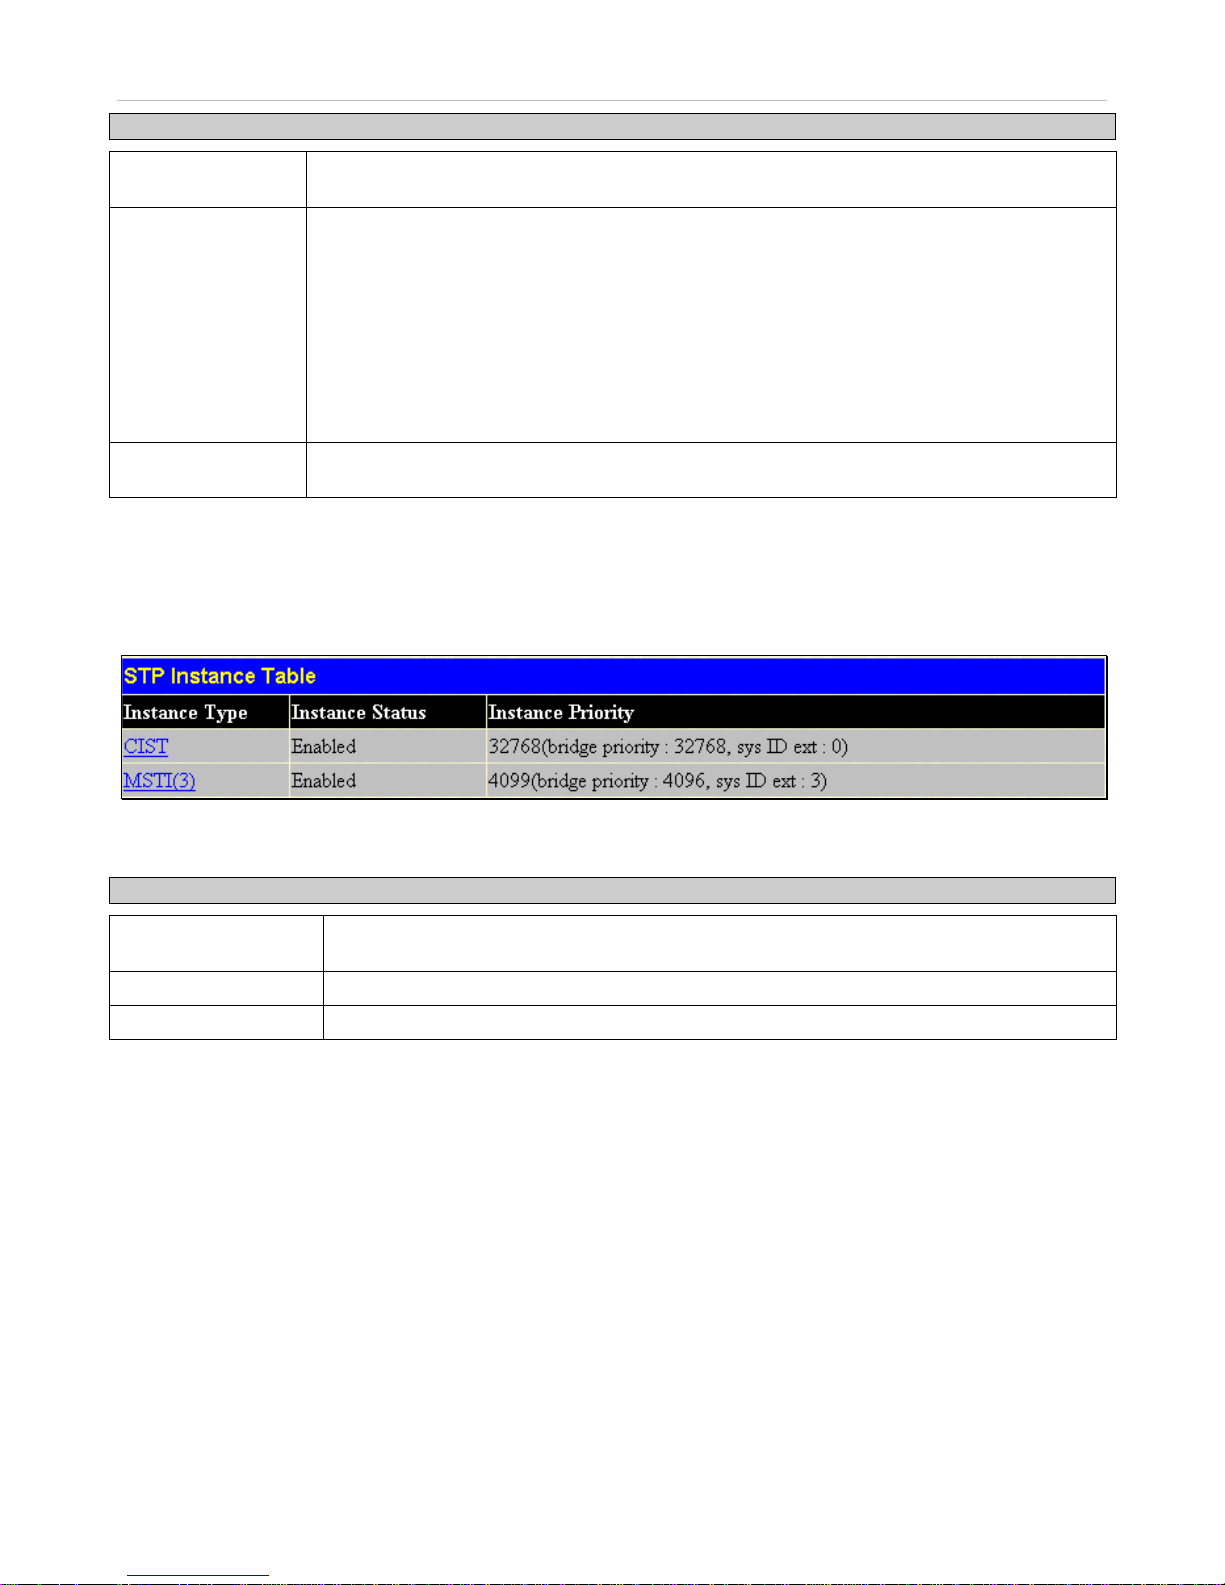
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
57
Parameter Description
Instance ID
Displays the MSTI ID of the instance being configured. An entry of 0 in this field denotes the
CIST (default MSTI).
Internal cost
(0=Auto)
This parameter is set to represent the relative cost of forwarding packets to specified ports
when an interface is selected within a STP instance. The default setting is 0 (auto). There are
two options:
• 0 (auto) - Selecting this parameter for the internalCost will set quickest route
automatically and optimally for an interface. The default value is derived from the
media speed of the interface.
• value 1-2000000 - Selecting this parameter with a value in the range of 1-2000000
will set the quickest route when a loop occurs. A lower Internal cost represents a
quicker transmission.
Priority
Enter a value between 0 and 240 to set the priority for the port interface. A higher priority will
designate the interface to forward packets first. A lower number denotes a higher priority.
Click Apply to implement changes made.
STP Instance Settings
The following window displays MSTIs currently set on the Switch. To view the following table, click Configuration > Spanning
Tree > STP Instance Settings:
Figure 6- 32. STP Instance Table window
The following information is displayed:
Parameter Description
Instance Type
Displays the instance type(s) currently configured on the Switch. Each instance type is
classified by a MSTI ID. CIST refers to the default MSTI configuration set on the Switch.
Instance Status
Displays the current status of the corresponding MSTI ID
Instance Priority
Displays the priority of the corresponding MSTI ID. The lowest priority will be the root bridge.
Click Apply to implement changes made.
To acquire more detailed information on a particular STP Instance, click its hyperlinked Instance Type, which will display the
following read-only window.
Page 73
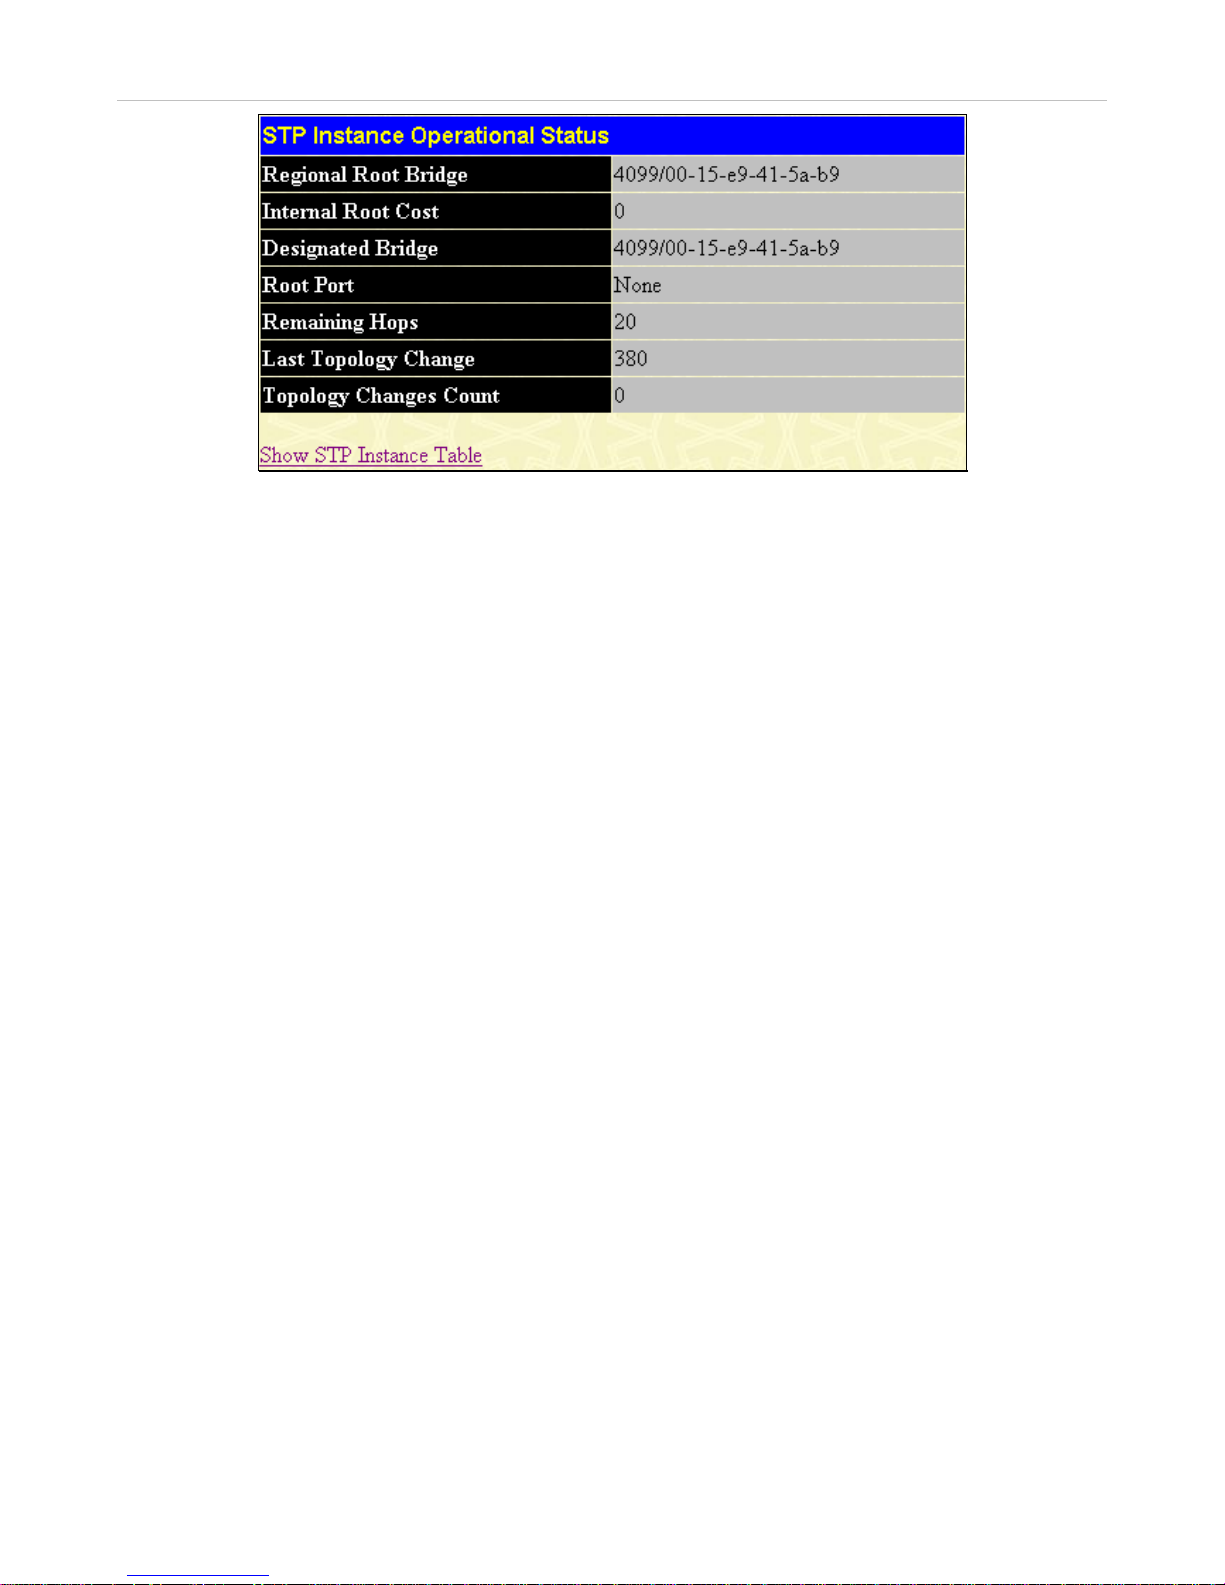
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
58
Figure 6- 33. STP Instance Operational Status
Page 74
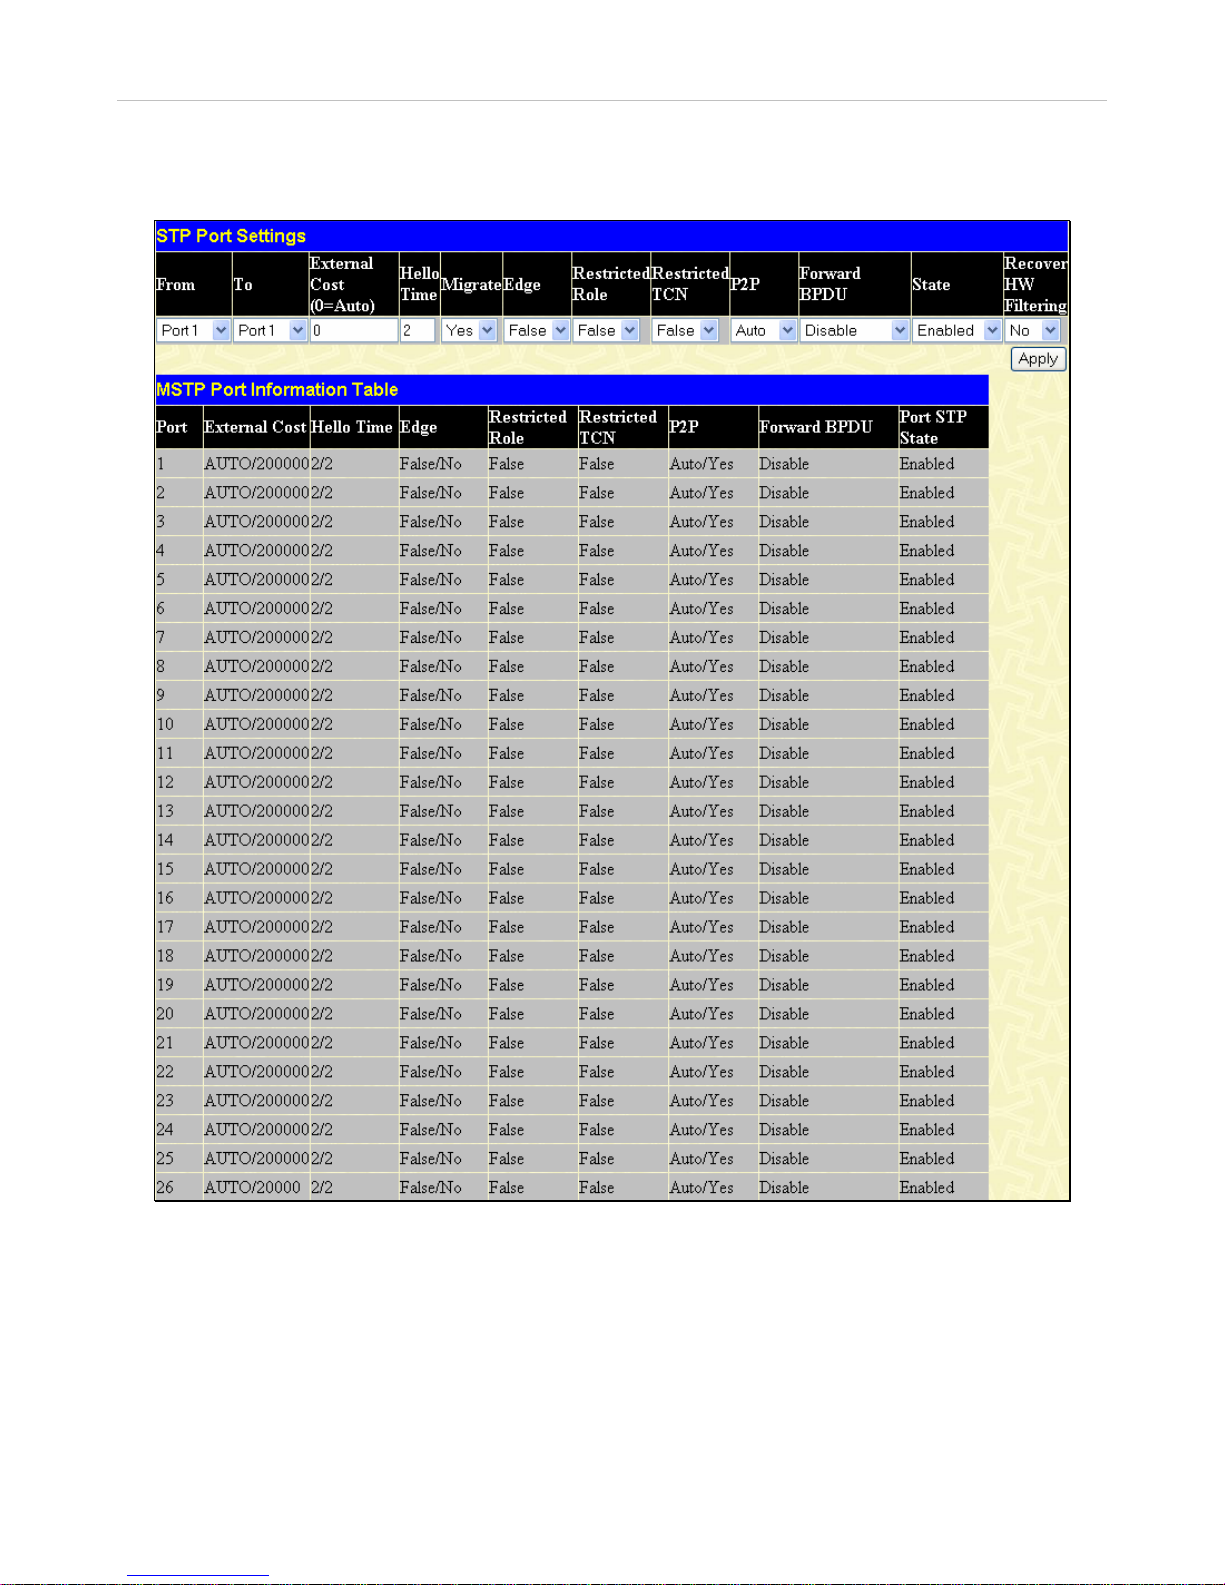
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
59
MSTP Port Information
STP can be set up on a port per port basis. To view the following window click Configuration > Spanning Tree > MSTP Port
Information:
Figure 6- 34. STP Port Settings window
In addition to setting Spanning Tree parameters for use on the switch level, the Switch allows for the configuration of groups of
ports, each port-group of which will have its own spanning tree, and will require some of its own configuration settings. An STP
Group will use the switch-level parameters entered above, with the addition of Port Priority and Port Cost.
An STP Group spanning tree works in the same way as the switch-level spanning tree, but the root bridge concept is replaced with
a root port concept. A root port is a port of the group that is elected based on port priority and port cost, to be the connection to the
network for the group. Redundant links will be blocked, just as redundant links are blocked on the switch level.
The STP on the switch level blocks redundant links between switches (and similar network devices). The port level STP will
block redundant links within an STP Gr o up .
It is advisable to define an STP Group to correspond to a VLAN group of ports.
Page 75
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
60
NOTE: If you want to enable Forwarding BPDU on a per port basis, the following settings must first be
in effect: 1. STP must be globally disabled and 2. Forwarding BPDU must be globally enabled. These
are the default settings configurable in the STP Bridge Global Settings menu discussed previously.
The following STP Port Settings fields can be set:
Parameter Description
From/To
A consecutive group of ports may be configured starting with the selected port.
External Cost
This defines a metric that indicates the relative cost of forwarding packets to the specified port
list. Port cost can be set automatically or as a metric value. The default value is 0 (auto).
0 (auto) - Setting 0 for the external cost will automatically set the speed for forwarding packets
to the specified port(s) in the list for optimal efficiency. Default port cost: 100Mbps port =
200000. Gigabit port = 20000.
value 1-200000000 - Define a value between 1 and 200000000 to determine the external cost.
The lower the number, the greater the probability the port will be chosen to forward packets.
Hello Time
The time interval between transmissions of configuration messages by the designated port, to
other devices on the bridged LAN. The user may choose a time between 1 and 2 seconds.
The default is 2 seconds. This field is only operable when the Switch is enabled for MSTP.
Migration
Setting this parameter as "yes" will set the ports to send out BPDU packets to other bridges,
requesting information on their STP setting If the Switch is configured for RSTP, the port will
be capable to migrate from 802.1d STP to 802.1w RSTP. If the Switch is configured for MSTP,
the port is capable of migrating from 802.1d STP to 802.1s MSTP. RSTP and MSTP can
coexist with standard STP, however the benefits of RSTP and MSTP are not realized on a port
where an 802.1d network connects to an 802.1w or 802.1s enabled network. Migration should
be set as yes on ports connected to network stations or segments that are capable of being
upgraded to 802.1w RSTP or 802.1s MSTP on all or some portion of the segment.
Edge
Choosing the True parameter designates the port as an edge port. Edge ports cannot create
loops, however an edge port can lose edge port status if a topology change creates a potential
for a loop. An edge port normally should not receive BPDU packets. If a BPDU packet is
received, it automatically loses edge port status. Choosing the False parameter indicates that
the port does not have edge port status.
Restricted Role
A Boolean value set by management. Two options are available for this parameter: Ture and
False. If TRUE causes the Port not to be selected as Root Port for the CIST or any MSTI, even
it has the best spanning tree priority vector. Such a Port will be selected as an Alternate Port
after the Root Port has been selected. This parameter should be FALSE by default. If set, it
can cause lack of spanning tree connectivity. It is set by a network administrator to prevent
bridges external to a core region of the network influencing the spanning tree active topology,
possibly because those bridges are not under the full control of the administrator.
Restricted Tcn
A Boolean value set by management. Two options are available for this parameter: Ture and
False. If TRUE causes the Port not to propagate received topology change notifications and
topology changes to other Ports. This parameter should be FALSE by default. If set it can
cause temporary loss of connectivity after changes in a spanning trees active topology as a
result of persistent incorrectly learned station location information. It is set by a network
administrator to prevent bridges external to a core region of the network, causing address
flushing in that region, possibly because those bridges are not under the full control of the
administrator or MAC_Operational for the attached LANs transitions frequently.
P2P
Choosing the True parameter indicates a point-to-point (P2P) shared link. P2P ports are
similar to edge ports, however they are restricted in that a P2P port must operate in full duplex.
Like edge ports, P2P ports transition to a forwarding state rapidly thus benefiting from RSTP. A
p2p value of False indicates that the port cannot have p2p status. Auto allows the port to have
p2p status whenever possible and operate as if the p2p status were true. If the port cannot
maintain this status, (for example if the port is forced to half-duplex operation) the p2p status
changes to operate as if the p2p value were false. The default setting for this parameter is
auto.
Forward BPDU
Choosing True will allow the forwarding of BPDU packets in the specified ports from other
network devices. This will go into effect only if STP is globally disabled AND Forwarding BPDU
Page 76
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
61
is globally enabled (See STP Bridge Global Settings above).
hw_filtering is an option that is only required by some legacy chipsets, which cannot support
per L2 protocol packet control. When the state is set to hw_filtering, if STP BPDU is received
by this port, the port will be changed to BPDU hardware filtering mode such that all layer 2
control packets will be dropped by the hardware.
The default setting False, does not forward BPDU packets when STP is disabled.
State
This drop-down menu allows you to enable or disable STP for the selected group of ports. The
default is Enabled.
Recover HW
Filtering
When a port is in BPDU hardware filtering mode, it can be recovered by this option.
Click Apply to implement changes made.
Page 77
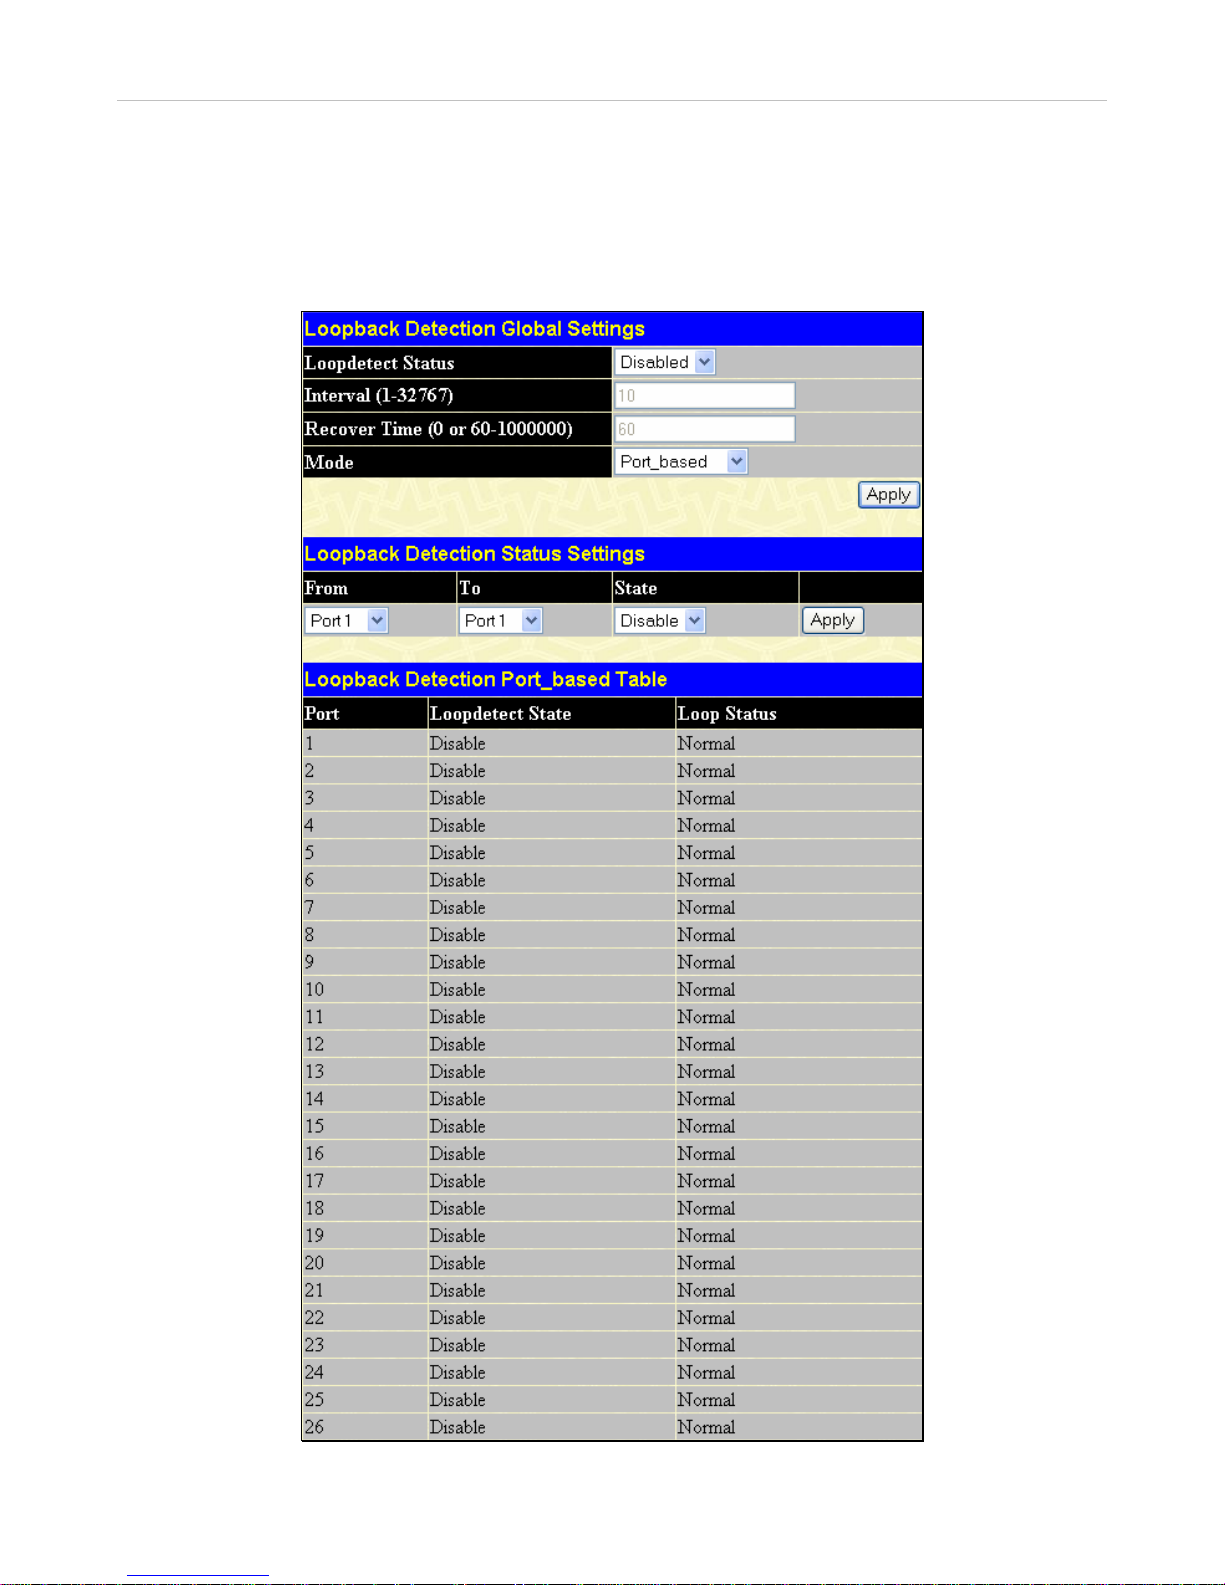
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
62
Loopback Detection
This feature is used to temporarily shutdown a port on the Switch when a CTP (Configuration Testing Protocol) packet has been
looped back to the switch. When the Switch detects CTP packets are received from a port or a VLAN, it signifies a loop on the
network. The Switch will automatically block the port or the VLAN and send an alert to the administrator. The Loopback
Detection port will restart (change to discarding state) when the Loopback Detection Recover Time times out. The Loopback
Detection function can be implemented on a range of ports at a time. The user may enable or disable this function using the pulldown menu. To view this window click, Configuration > Loopback Detection.
Figure 6- 35 Loopback Detection Global Settings window
Page 78
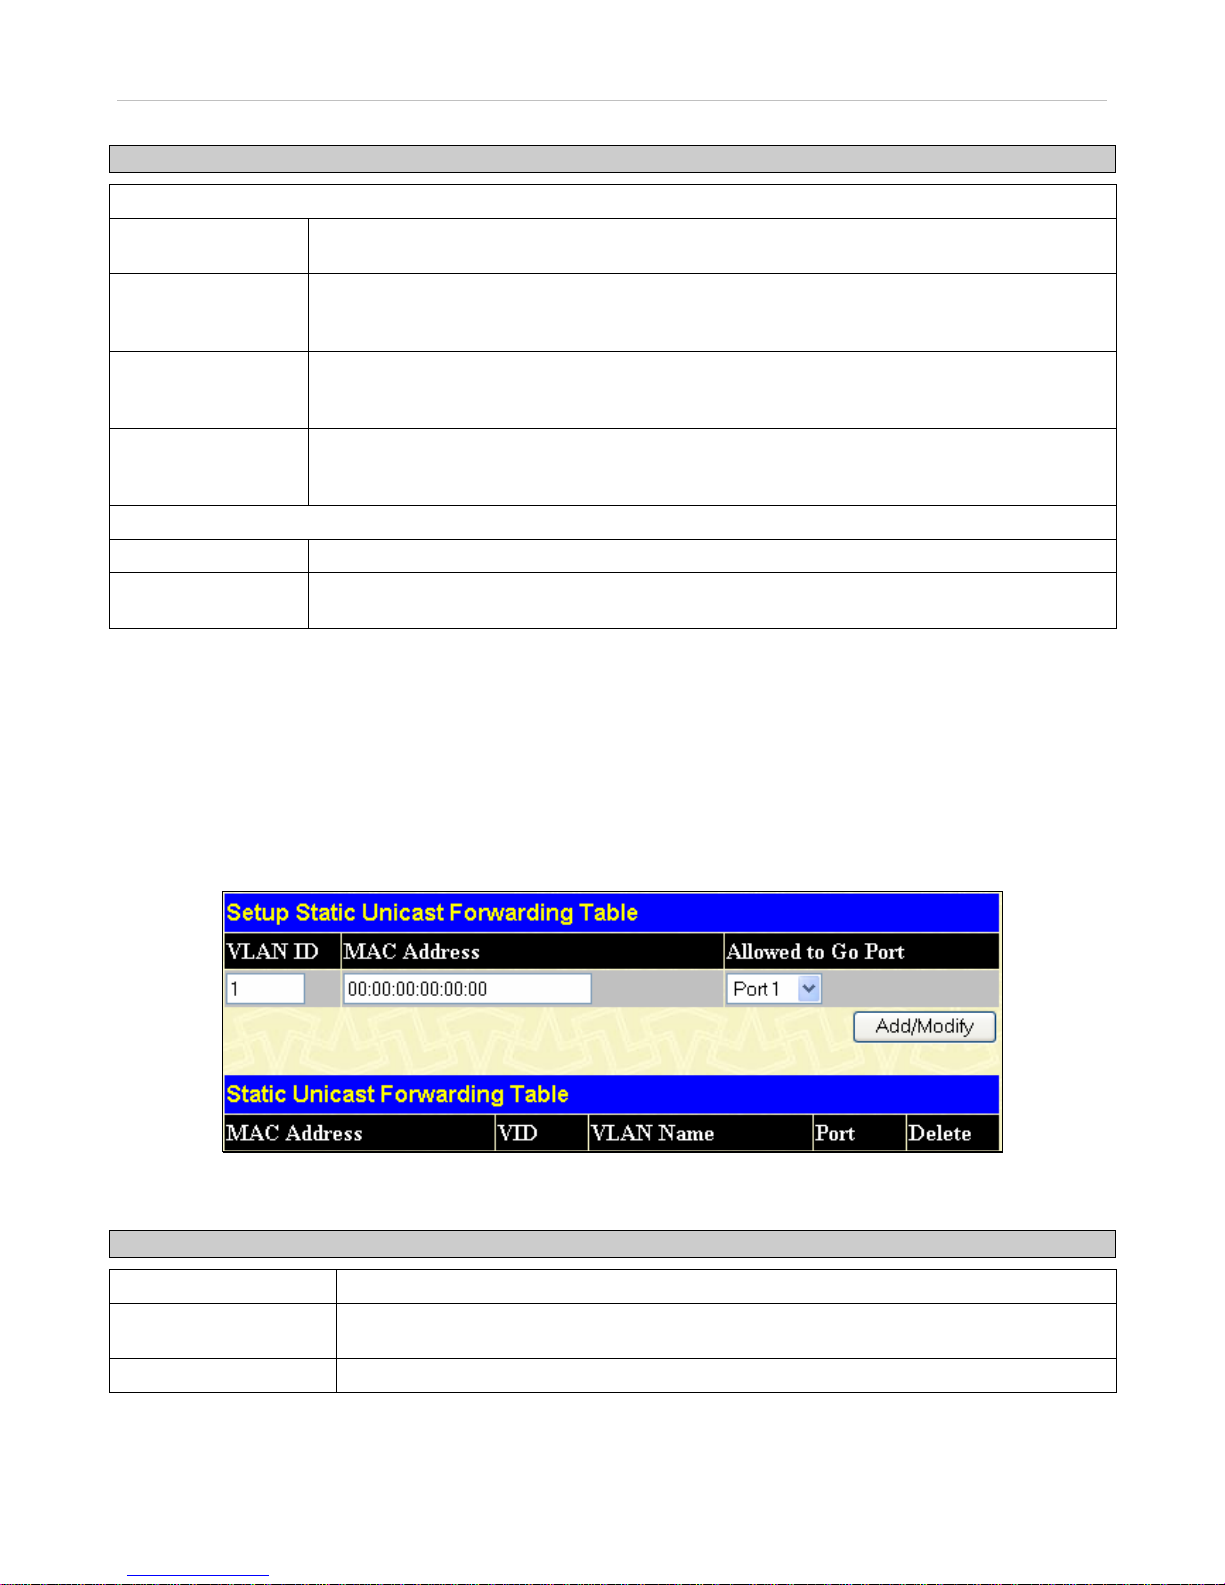
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
63
The following parameters can be set:
Parameter Description
Loopback Detection Global Settings
Loopback
Detection Status
Use the pull-down menu to enable or disable Loopback Detection globally on the Switch. The
default is Disabled.
Interval (1-32767)
Use the pull-down menu to set up the time interval (inseconds) at which the remote device
transmits all the CTP packets to detect the loop-back event. The default value is 10, with a
valid range of 1 to 32767,
Recover Time
(0 or 60 – 1000000)
The time interval (in seconds) used by the Auto-Recovery mechanism to decide how long to
check if the loop status is gone. The valid range is 60 to 1000000. Zero is a special value,
which means to disable the auto-recovery mechanism. The default value is 60.
Mode
Two modes are available: Port_based, VLAN_based. In port-based mode, the port will be
disabled during the loop detection. In vlan-based mode, the port cannot porcess VLAN
packets destined for ports involved in detecting the loop.
Loopback Detection Status Settings
From/To
A consecutive group of ports may be configured starting with the selected port.
State
Use the pull-down menu to enable or disable Loopback Detection on consecutive group of
ports of the Switch. The default is Disabled.
Click Apply to implement changes made.
Forwarding Filtering
Unicast Forwarding
Open the Forwarding Filtering folder in the Configuration menu and click on the Unicast Forwarding link. This will open the
Setup Static Unicast Forwarding Table, as shown below:
Figure 6- 36. Setup Static Unicast Forwarding Table window
To add or edit an entry, define the following parameters and then click Add/Modify:
Parameter Description
VLAN ID (VID)
The VLAN ID number of the VLAN on which the above Unicast MAC address resides.
MAC Address
The MAC address to which packets will be statically forwarded. This must be a unicast
MAC address.
Allowed to Go Port
Allows the selection of the port number on which the MAC address entered above resides.
Click Apply to implement the changes made. To delete an entry in the Static Unicast Forwarding Table, click the corresponding X
under the Delete heading.
Page 79
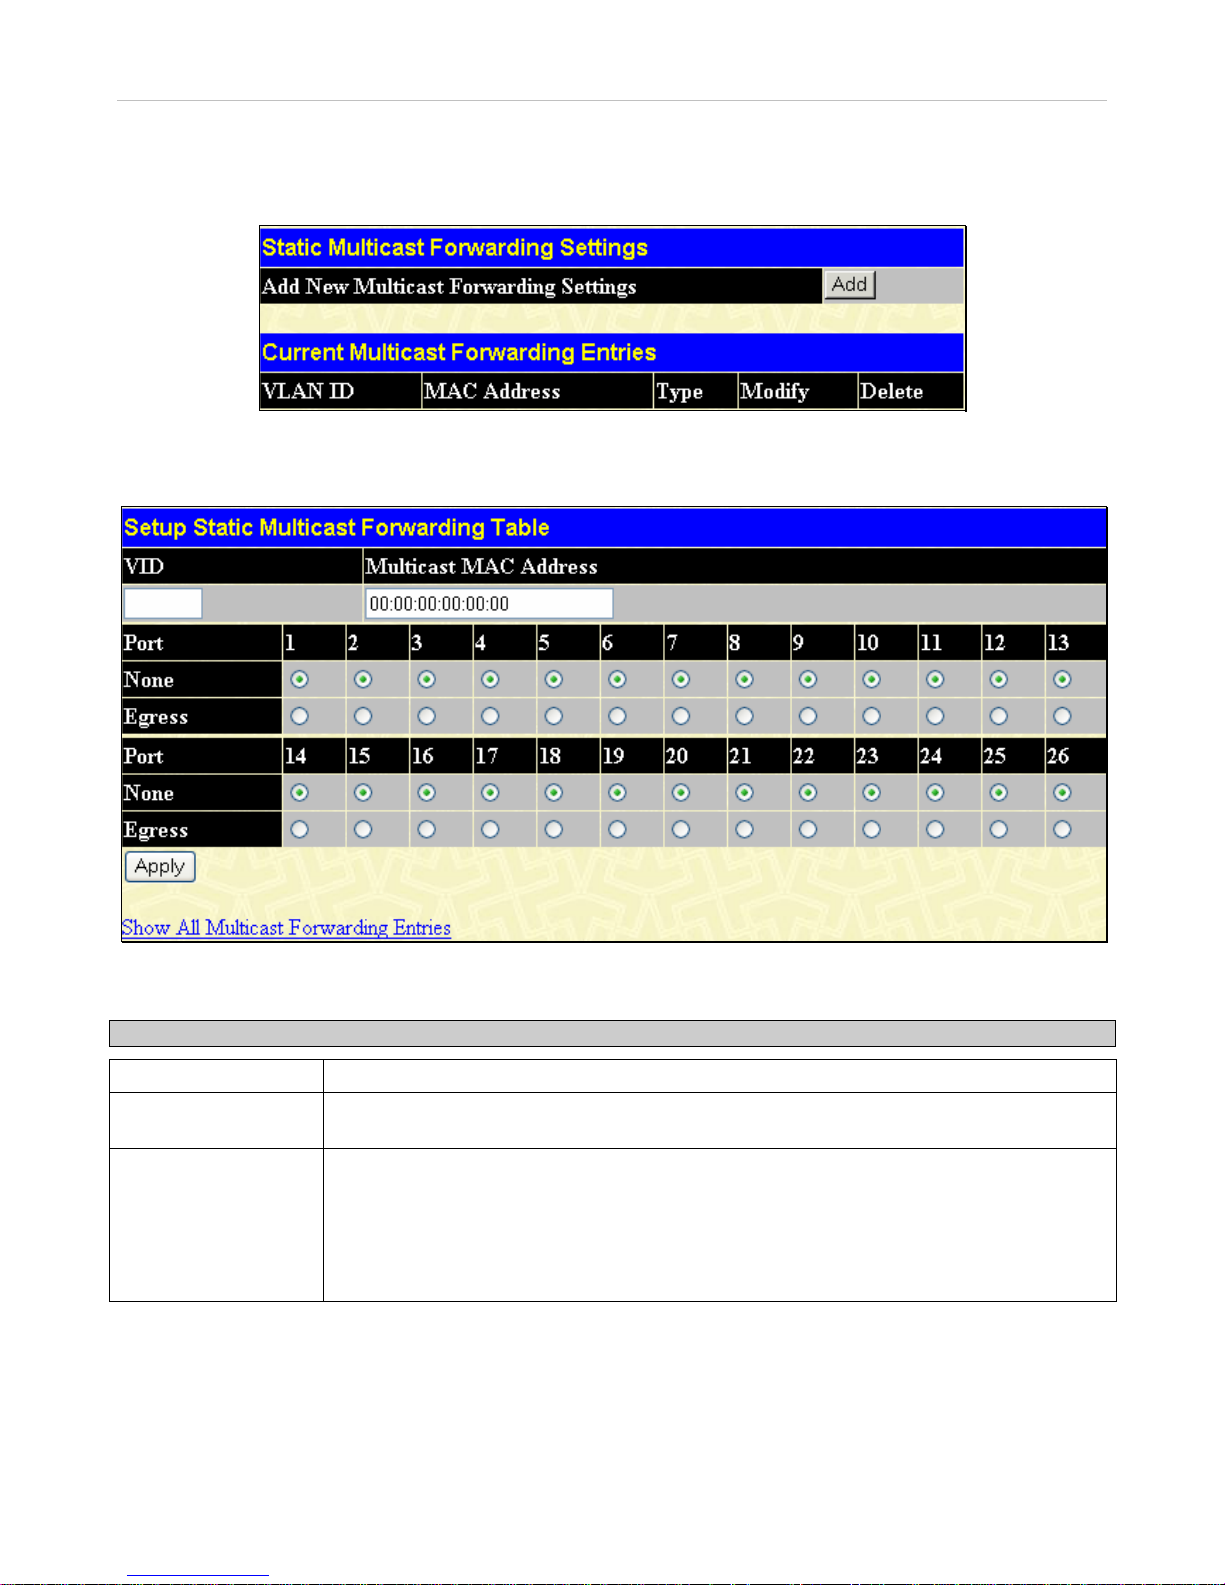
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
64
Multicast Forwarding
The following figure and table describe how to set up Multicast Forwarding on the Switch. To view this window click,
Configuration > Forwarding Filtering > Multicast Forwarding:
Figure 6- 37. Static Multicast Forwarding Settings window
The Static Multicast Forwa rding Settings window displays all of the entries made into the Switch's static multicast forwarding
table. Click the Add button to open the Setup Static Multicast Forwarding Table window, as shown below:
Figure 6- 38. Setup Static Multicast Forwarding Table window
The following parameters can be set:
Parameter Description
VID
The VLAN ID of the VLAN to which the corresponding MAC address belongs.
Multicast MAC
Address
The MAC address of the static source of multicast packets. This must be a multicast MAC
address.
Port Settings
Allows the selection of ports that will be members of the static multicast group and ports
either that are forbidden from joining dynamically, or that can join the multicast group
dynamically, using GMRP. The options are:
None - No restrictions on the port dynamically joining the multicast group. When None is
chosen, the port will not be a member of the Static Multicast Group.
Egress - The port is a static member of the multicast group.
Click Apply to implement the changes made. To delete an entry in the Static Multicast Fo rwarding Table, click the correspo nding
X under the Delete heading. Click the Show All Multicast Forwarding Entries link to return to the Static Multicast
Forwarding Settings window.
Page 80
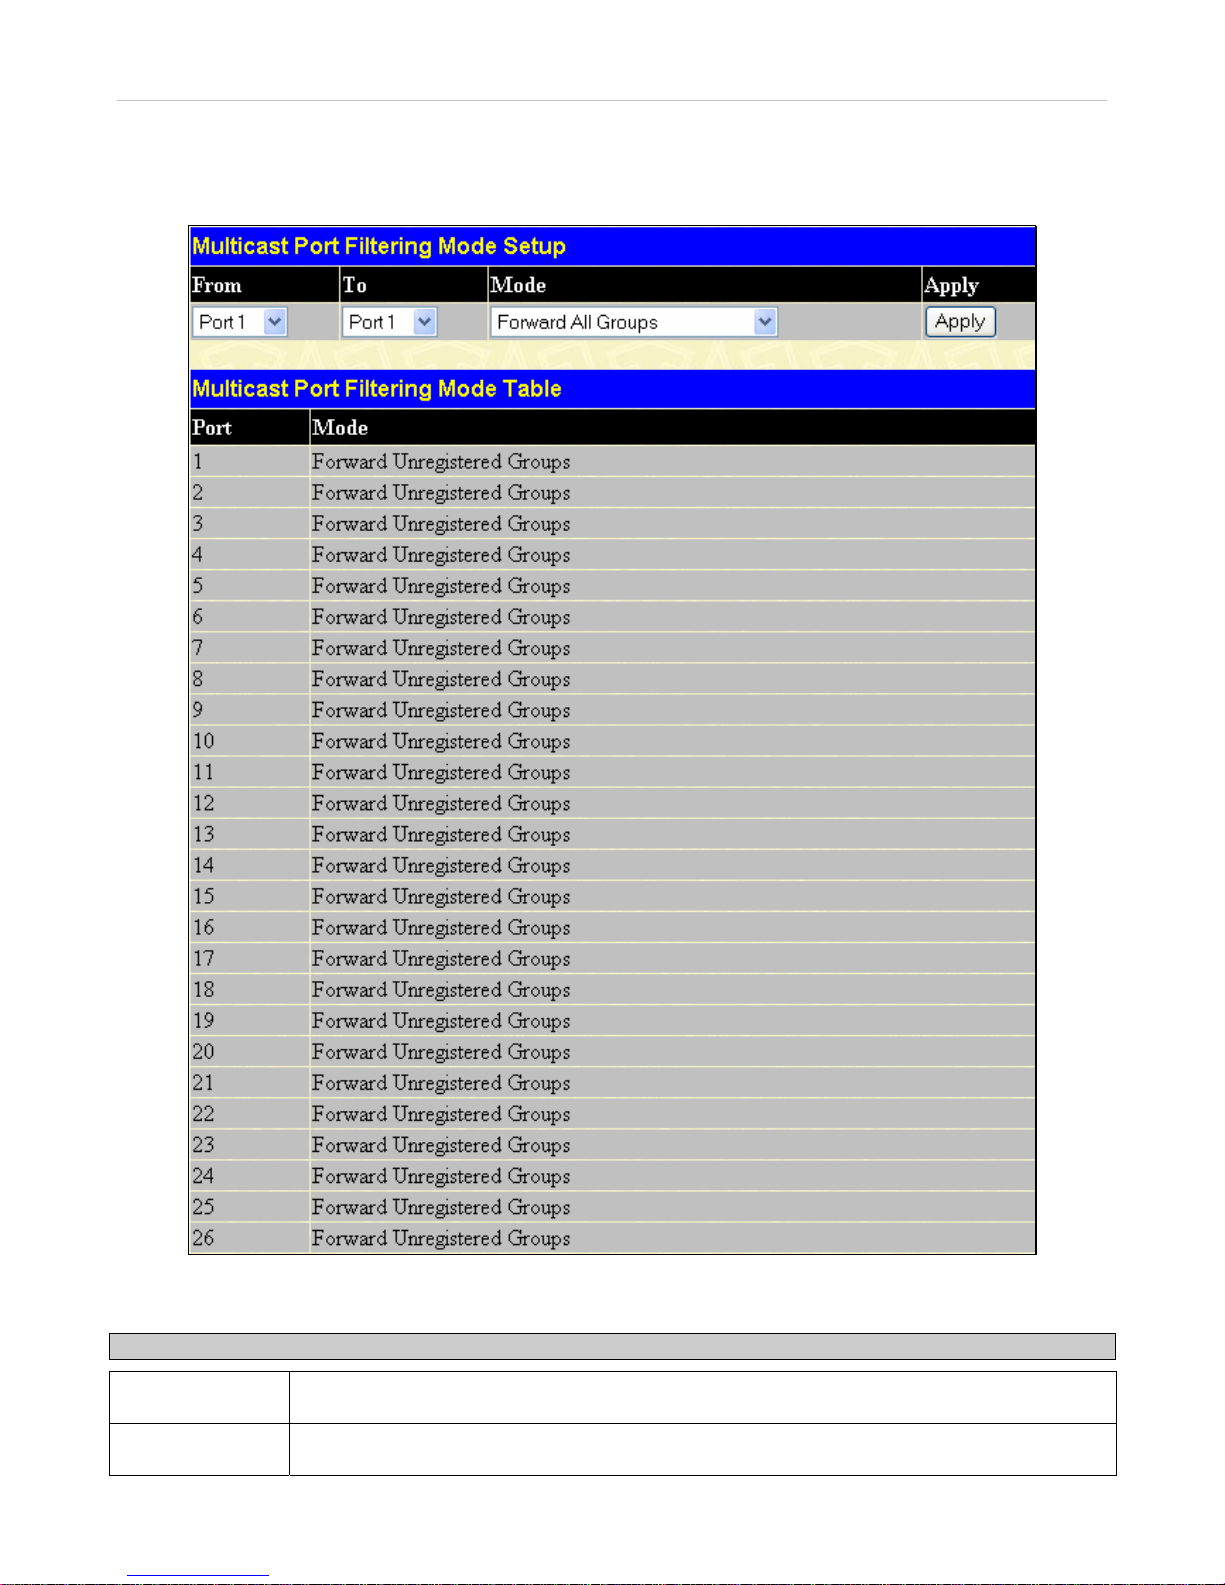
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
65
Multicast Port Filtering Mode
The following figure and table describe how to set up multicast forwarding on the Switch. To view this window click,
Configuration > Forwarding Filtering > Multicast Port Filtering Mode Setup.
Figure 6- 39. Multicast Port Filtering Mode Setup window
The following parameters can be set:
Parameter Description
From/To
These two drop-down menus allow you to select a range of ports to which the filter settings will
be applied.
Mode
This drop-down menu allows you to select the action the Switch will take when it receives a
multicast packet that is to be forwarded to one of the ports in the range specified above.
Page 81
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
66
• Forward All Groups - This will instruct the Switch to forward a multicast packet to all
multicast groups residing within the range of ports specified above.
• Forward Unregistered Groups - This will instruct the Switch to forward a multicast
packet whose destination is an unregistered multicast group residing within the range
of ports specified above.
• Filter Unregistered Groups - This will instruct the Switch to filter any multicast packets
whose destination is an unregistered multicast group residing within the range of ports
specified above.
Click Apply to implement changes made.
Page 82
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
67
VLANs
Understanding IEEE 802.1p Priority
Priority tagging is a function defined by the IEEE 802.1p standard designed to provide a means of managing traffic on a network
where many different types of data may be transmitted simultaneously. It is intended to alleviate problems associated with the
delivery of time critical data over congested networks. The quality of applications th at are dependent on such time critical data,
such as video conferencing, can be severely and adversely affected by even very small delays in transmission.
Network devices that are in compliance with the IEEE 802.1p standard have the ability to recognize the priority level of d ata
packets. These devices can also assign a priority label or tag to packets. Compliant devices can also strip priority tags from
packets. This priority tag determines the packet's degree of expeditiousness and determines the queue to which it will be assigned.
Priority tags are given values from 0 to 7 with 0 being assigned to the lowest priority data and 7 assigned to the highest. The
highest priority tag 7 is generally only used for data associated with video or audio app lications, which are sensitive to even slight
delays, or for data from specified end users whose data transmissions warrant special consideration.
The Switch allows you to further tailor how priority tagged data packets are handled on your network. Using queues to manage
priority tagged data allows you to specify its relative priority to suit the needs of your network. There may be circumstances where
it would be advantageous to group two or more differently tagged packets into the same queue. Generally, however, it is recommended that the highest priority queue, Queue 1, be reserved for data packets with a priority value of 7. Packets that have not
been given any priority value are placed in Queue 0 and thus given the lowest priority for delivery.
A weighted round robin system is employed on the Switch to determine the rate at which the queues are emptied of packets. The
ratio used for clearing the queues is 4:1. This means that the highest priority queue, Queue 1, will clear 4 packets for every 1
packet cleared from Queue 0.
Remember, the priority queue settings on the Switch are for all ports, and all devices connected to the Switch will be affected.
This priority queuing system will be especially beneficial if your network employs switches with the capability of assigning
priority tags.
VLAN Description
A Virtual Local Area Network (VLAN) is a network topology con figured according to a logical scheme rather th an the physical
layout. VLANs can be used to combine any collection of LAN segments into an autonomous user group that appears as a single
LAN. VLANs also logically segment the network into different broadcast domains so that packets are forwarded only between
ports within the VLAN. Typically, a VLAN corresponds to a particular subnet, although not necessarily.
VLANs can enhance performance by conserving bandwidth, and improve security by limiting traffic to specific domains.
A VLAN is a collection of end nodes grouped by logic instead of physical location. End nodes that frequently communicate with
each other are assigned to the same VLAN, regardless of where they are physically on the network. Logically, a VLAN can be
equated to a broadcast domain, because broadcast packets are forwarded to only members of the VLAN on which the broadcast
was initiated.
Notes about VLANs on the xStack® DES-3500 Series switches
No matter what basis is used to uniquely identify end nodes and assign these nodes VLAN membership, packets cannot cross
VLANs without a network device performing a routing function between the VLANs.
The DES-3500 Series switches supports IEEE 802.1Q VLANs and Port-Based VLANs. The port untagging function can be used
to remove the 802.1Q tag from packet headers to maintain compatibility with devices that are tag-unaware.
The Switch's default is to assign all ports to a single 802.1Q VLAN named "default."
The "default" VLAN has a VID = 1.
The member ports of Port-based VLANs may overlap, if desired.
IEEE 802.1Q VLANs
Some relevant terms:
• Tagging - The act of putting 802.1Q VLAN information into the header of a packet.
• Untagging - The act of stripping 802.1Q VLAN information out of the packet header.
• Ingress port - A port on a switch where packets are flowing into the Switch and VLAN decisions must
be made.
• Egress port - A port on a switch where packets are flowing out of the Switch, either to another switch
or to an end station, and tagging decisions must be made.
Page 83
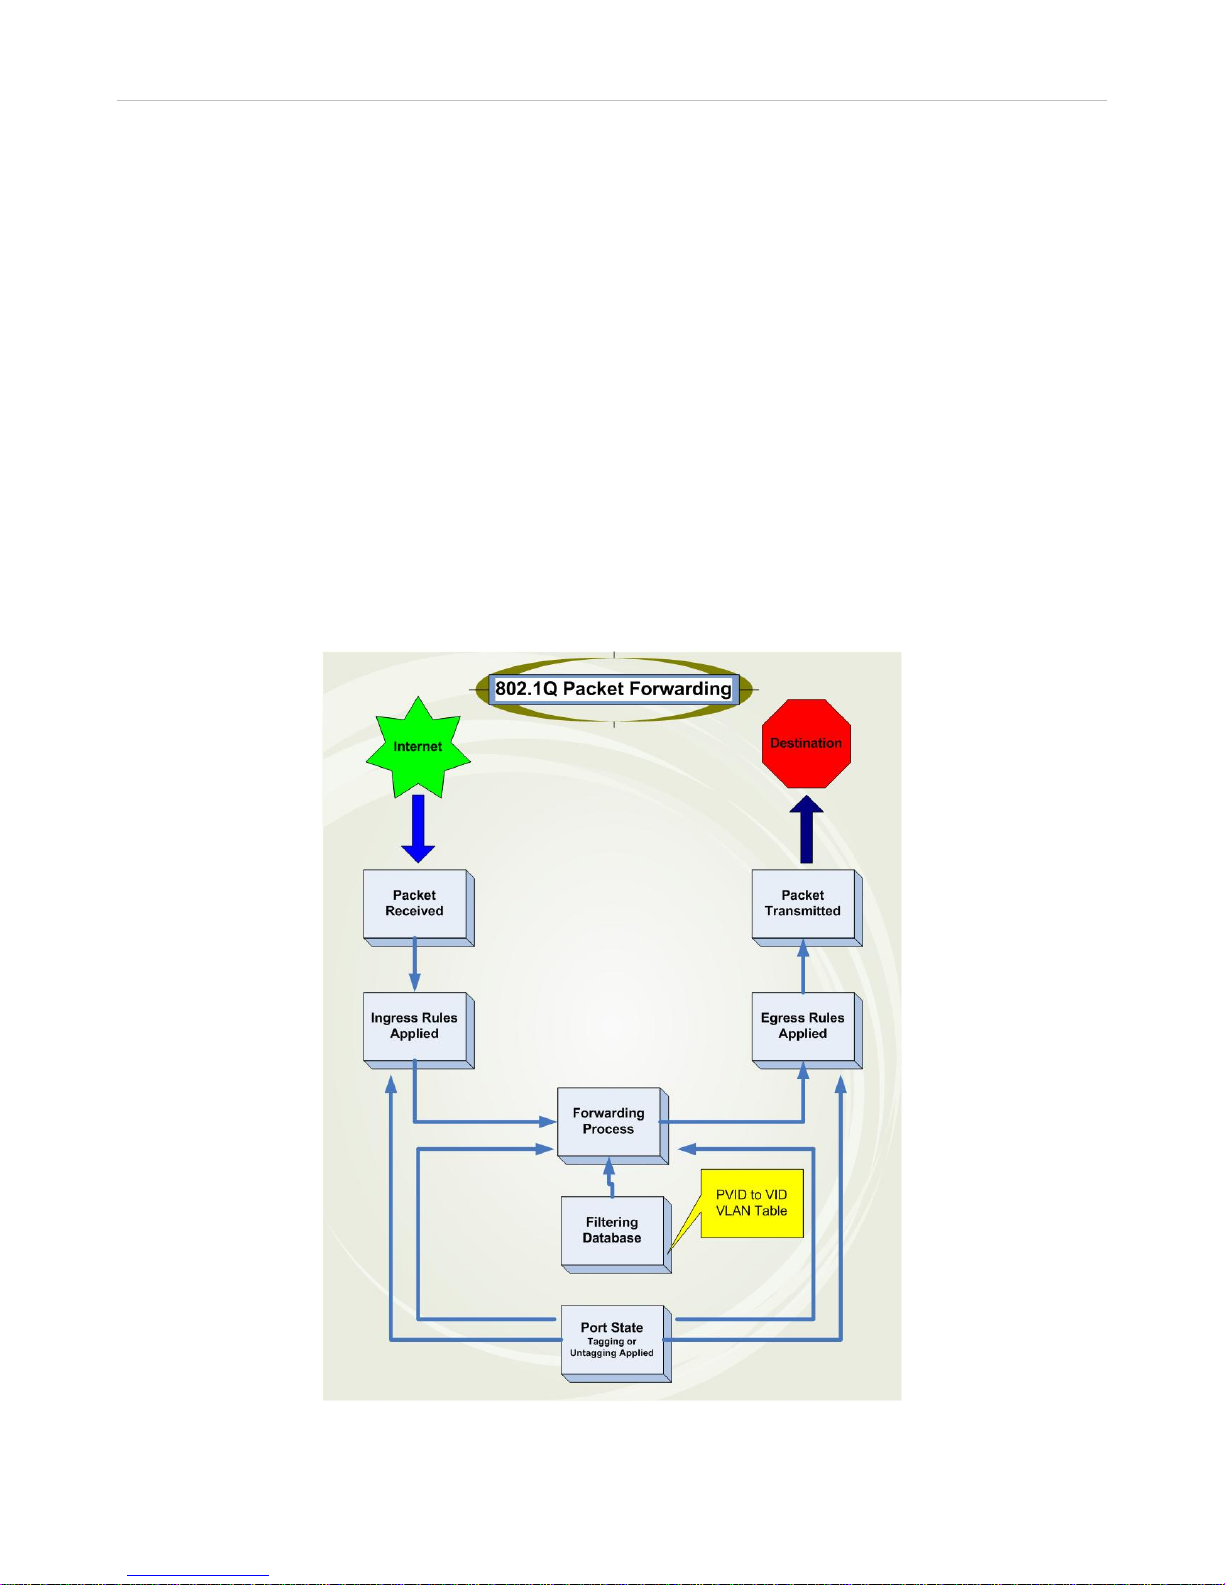
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
68
IEEE 802.1Q (tagged) VLANs are implemented on the Switch. 802.1Q VLANs require tagging, which enables them to span the
entire network (assuming all switches on the network are IEEE 802.1Q-compliant).
VLANs allow a network to be segmented in order to reduce the size of broadcast domains. All pack ets entering a VLAN will only
be forwarded to the stations (over IEEE 802.1Q enabled switch es) that are members of that VLAN, and this includes broadcast,
multicast and unicast packets from unknown sources.
VLANs can also provide a level of security to your network. IEEE 802.1Q VLANs will only deliver packets between stations that
are members of the VLAN.
Any port can be configured as either tagging or untagging. The untagging feature of IEEE 802.1Q VLANs allows VLANs to work
with legacy switches that don't recognize VLAN tags in packet headers. The tagging feature allows VLANs to span multiple
802.1Q-compliant switches through a single physical connection and allows Spanning Tree to be enabled on all ports and work
normally.
The IEEE 802.1Q standard restricts the forwarding of untagged packets to the VLAN the receiving port is a member of.
The main characteristics of IEEE 802.1Q are as follows:
• Assigns packets to VLANs by filtering.
• Assumes the presence of a single global spanning tree.
• Uses an explicit tagging scheme with one-level tagging.
• 802.1Q VLAN Packet Forwarding
• Packet forwarding decisions are made based upon the following three types of rules:
• Ingress rules - rules relevant to the classification of received frames belonging to a VLAN.
• Forwarding rules between ports - decides whether to filter or forward the packet.
• Egress rules - determines if the packet must be sent tagged or untagged.
Figure 6- 40. IEEE 802.1Q Packet Forwarding
Page 84
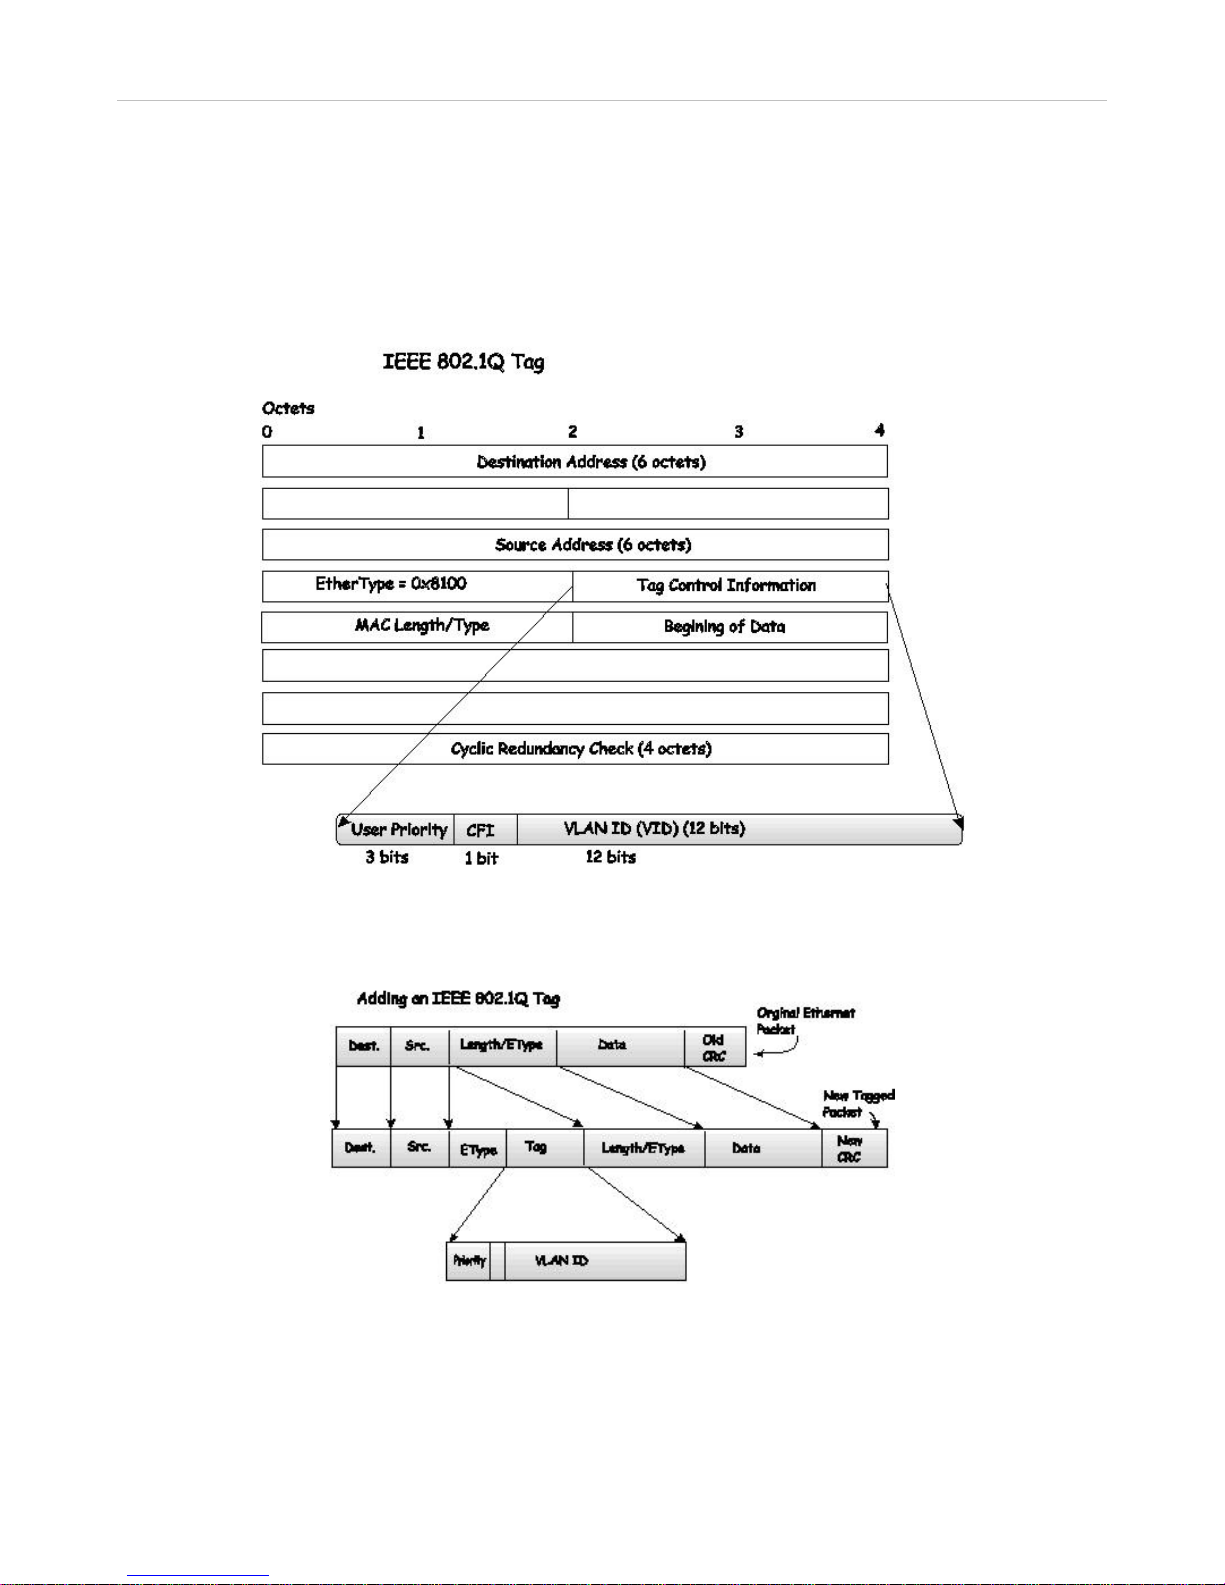
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
69
802.1Q VLAN Tags
The figure below shows the 802.1Q VLAN tag. There are four additional octets inserted after the source MAC address. Their
presence is indicated by a value of 0x8100 in the EtherType field. When a packet's EtherTyp e field is equal to 0x8100, the packet
carries the IEEE 802.1Q/802.1p tag. The tag is contained in the following two octets and consists of 3 bits of user priority, 1 bit o f
Canonical Format Identifier (CFI - used for encapsulating Token Ring packets so they can be carried across Ethernet backbones),
and 12 bits of VLAN ID (VID). The 3 bits of user priority are used by 802.1p. The VID is the VLAN identifier and is used by the
802.1Q standard. Because the VID is 12 bits long, 4094 unique VL A Ns can be ide nti fi ed .
The tag is inserted into the packet header making the entire packet longer by 4 octets. All of the information originally contained
in the packet is retained.
Figure 6- 41. IEEE 802.1Q Tag
The EtherType and VLAN ID are inserted after the MAC source address, but before the original EtherType/Length or Logical
Link Control. Because the packet is now a bit longer than it was originally, the Cyclic Redundancy Check (CRC) must be
recalculated.
Figure 6- 42. Adding an IEEE 802.1Q Tag
Port VLAN ID
Packets that are tagged (are carrying the 802.1Q VID information) can be transmitted from one 802.1Q compliant network device
to another with the VLAN information intact. This allows 802.1Q VLANs to span network devices (and indeed, the entire
network, if all network devices are 802.1Q compliant).
Page 85
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
70
Unfortunately, not all network devices are 802.1Q compliant. These devices are referred to as tag-unaware. 802.1Q devices are
referred to as tag-aware.
Prior to the adoption of 802.1Q VLANs, port-based and MAC-based VLANs were in common use. These VLANs relied upon a
Port VLAN ID (PVID) to forward packets. A packet received on a given port would be assigned that port's PVID and then be
forwarded to the port that corresponded to the packet's destination address (found in the Switch's forwarding table). If the PVID of
the port that received the packet is different from the PVID of the port that is to transmit the packet, the Switch will drop the
packet.
Within the Switch, different PVIDs mean different VLANs (remember that two VLANs cannot communicate without an external
router). So, VLAN identification based upon the PVIDs cannot create VLANs that extend outside a given switch (or switch stack).
Every physical port on a switch has a PVID. 802.1Q ports are also assigned a PVID, for use within the Switch. If no VLANs are
defined on the Switch, all ports are then assigned to a default VLAN with a PVID equal to 1. Untagged packets are assigned the
PVID of the port on which they were received. Forwarding decisions are based upon this PVID, in so far as VLANs are concerned.
Tagged packets are forwarded according to the VID contained within the tag. Tagged packets are also assigned a PVID, but the
PVID is not used to make packet-forwarding decisions, the VID is.
Tag-aware switches must keep a table to relate PVIDs within the Switch to VIDs on the network. The Switch will compare the
VID of a packet to be transmitted to the VID of the port that is to transmit the packet. If the two VIDs are different, the Switch
will drop the packet. Because of the existence of the PVID for untagged packets and the VID for tag ged packets, tag-aware and
tag-unaware network devices can coexist on the same network.
A switch port can have only one PVID, but can have as many VIDs as the Switch has memory in its VLAN table to store them.
Because some devices on a network may be tag-unaware, a decision must be made at each port on a tag-aware device before
packets are transmitted - should the packet to be transmitted have a tag or not? If the transmitting port is conn ected to a tagunaware device, the packet should be untagged. If the transmitting port is connected to a tag-aware device, the packet should be
tagged.
Tagging and Untagging
Every port on an 802.1Q compliant swit c h c an be c on fi g ur ed as tag gi n g o r untagging.
Ports with tagging enabled will put the VID nu mber, priority and oth er VLAN information into the header of all packets that flow
into and out of it. If a packet has previously been tagged, the port will not alter the packet, thus keeping the VLAN information
intact. Other 802.1Q compliant devices on the network to make packet-forwarding decisions can then use the VLAN information
in the tag.
Ports with untagging enabled will strip the 802.1Q tag from all packets that flow into and out of those ports. If the packet do esn't
have an 802.1Q VLAN tag, the port will not alter the packet. Thus, all packets received by and forwarded by an untagging port
will have no 802.1Q VLAN information. (Remember that the PVID is only used internally within the Switch). Untagging is used
to send packets from an 802.1Q-compliant network device to a non-compliant network device.
Ingress Filtering
A port on a switch where packets are flowing into the Switch and VLAN decisions must be made is referred to as an ingress port.
If ingress filtering is enabled for a port, the Switch will examine the VLAN information in the packet head er (if present) and
decide whether or not to forward the packet.
If the packet is tagged with VLAN information, the ingress port will first determine if the ingress port itself is a member of the
tagged VLAN. If it is not, the packet will be dropped. If the ingress port is a member of the 802.1Q VLAN, the Switch then
determines if the destination port is a member of the 802.1Q VLAN. If it is not, the packet is dropp ed. If the destination port is a
member of the 802.1Q VLAN, the packet is forwarded and the destination port transmits it to its attached network segment.
If the packet is not tagged with VLAN information, the ingress port will tag th e packet with its own PVID as a VID (if the po rt is
a tagging port). The switch then determines if the destination port is a member of the same VLAN (has the same VID) as the
ingress port. If it does not, the packet is dropped. If it has the same VID, the packet is forwarded and the destination port transmits
it on its attached network segment.
This process is referred to as ingress filtering and is used to conserve bandwidth within the Switch by dropping packets th at are
not on the same VLAN as the ingress port at the point of reception. This eliminates the subsequent processing of packets that will
just be dropped by the destination port.
Default VLANs
The Switch initially configures one VLAN, VID = 1, called "default." The factory default setting assigns all ports on the Switch to
the "default." As new VLANs are configured in Port-based mode, their respective member ports are removed from the "default."
Packets cannot cross VLANs. If a member of one VLAN wants to connect to another VLAN, the link must be through an external
router.
Page 86
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
71
NOTE: If no VLANs are configured on the Switch, then all packets will be forwarded to any destination port. Packets with unknown source addresses will be flooded to all ports. Broadcast and
multicast packets will also be flooded to all ports.
An example is presented below:
VLAN Name VID Switch Ports
System (default) 1 5, 6, 7, 8, 21, 22, 23, 24
Engineering 2 9, 10, 11, 12
Marketing 3 13, 14, 15, 16
Finance 4 17, 18, 19, 20
Sales 5 1, 2, 3, 4
Table 6- 2. VLAN Example - Assigned Ports
Port-based VLANs
Port-based VLANs limit traffic that flows into and out of switch ports. Thus, all devices connected to a port are members of the
VLAN(s) the port belongs to, whether there is a single computer directly connected to a switch, or an entire department.
On port-based VLANs, NICs do not need to be able to identify 802.1Q tags in packet headers. NICs send and receive normal
Ethernet packets. If the packet's destination lies on the same segment, communications take place using normal Ethernet protocols.
Even though this is always the case, when the destination for a packet lies on another switch port, VLAN considerations come into
play to decide if the packet gets dropped by the Switch or delivered.
VLAN Segmentation
Take for example a packet that is transmitted by a machine on Port 1 that is a member of VLAN 2. If the destination lies on
another port (found through a normal forwarding table lookup), the Switch then looks to see if the other port (Port 10) is a member
of VLAN 2 (and can therefore receive VLAN 2 packets). If Port 10 is not a member of VLAN 2, then the packet will be dropped
by the Switch and will not reach its destination. If Port 10 is a member of VLAN 2, the packet will go through. This selective
forwarding feature based on VLAN criteria is how VLANs segment networks. The key point being that Port 1 will only transmit
on VLAN 2.
Page 87
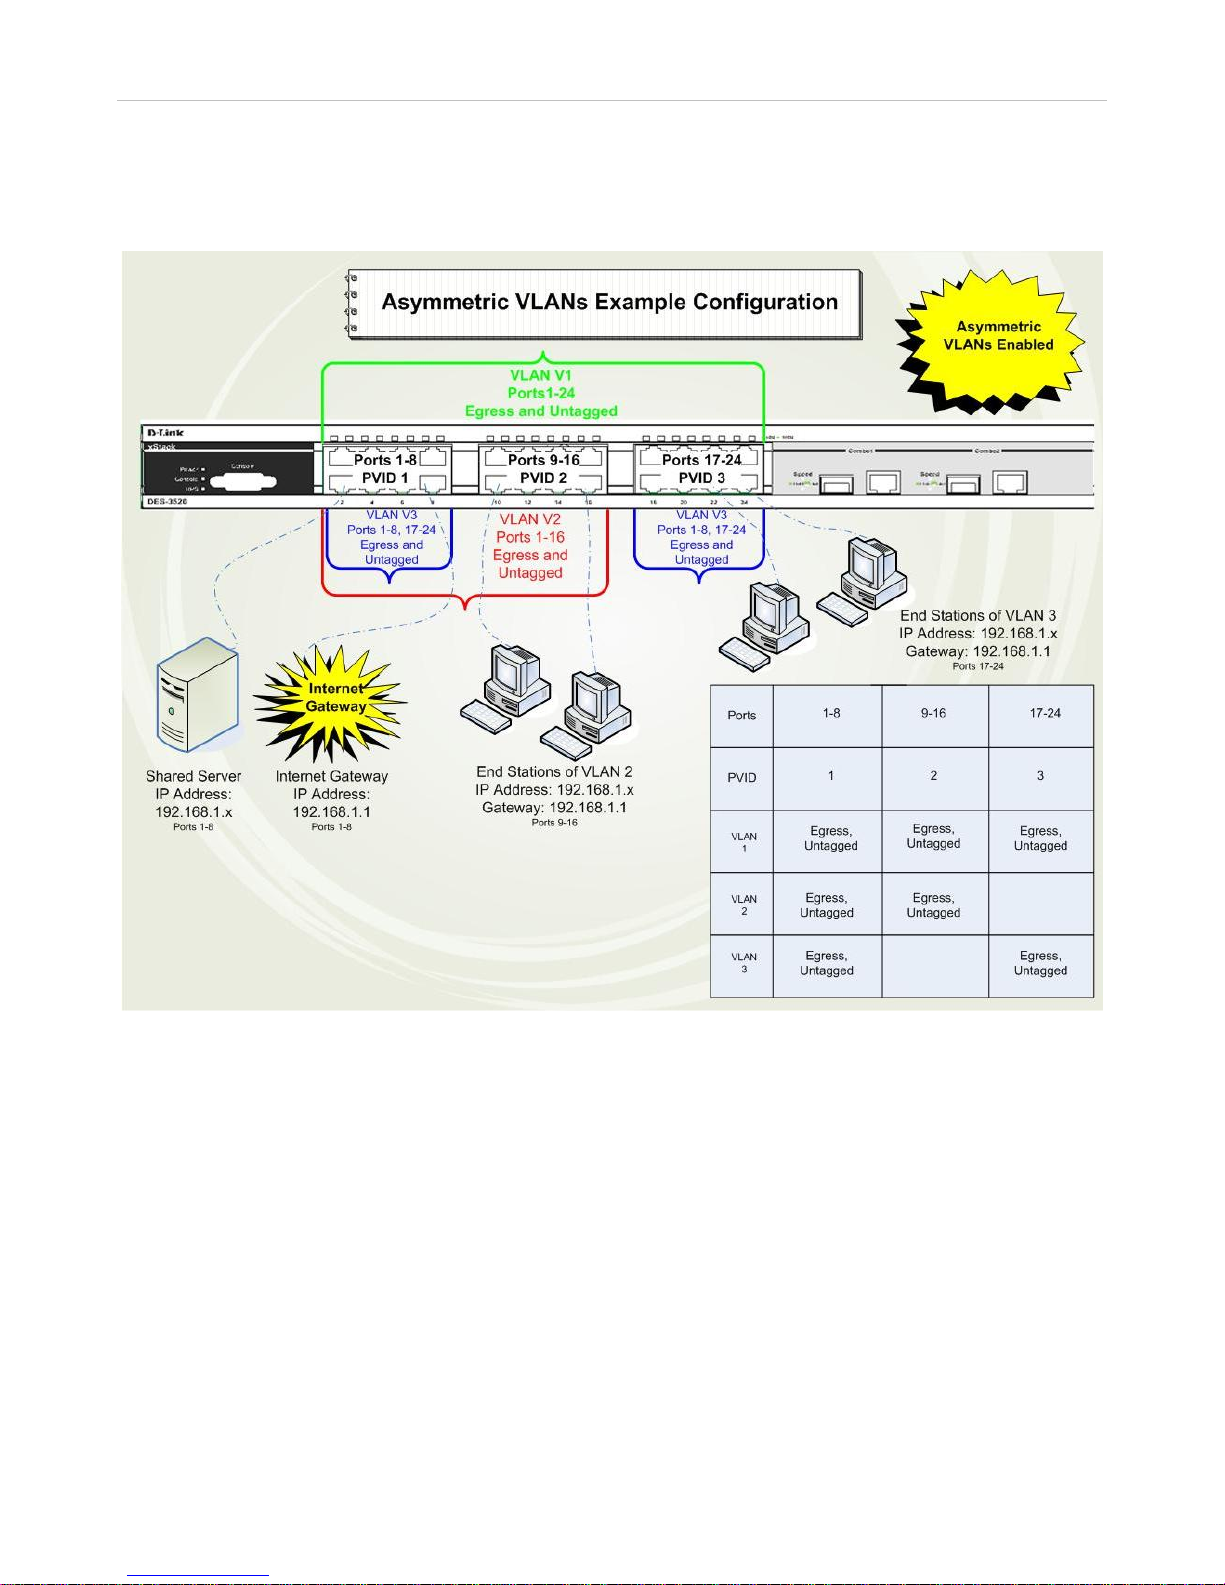
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
72
Asymmetric VLANs
The xStack® DES-3500 Switch Series has the capability to create and utilize Asymmetric VLANs on the Switch. Asymmetric
VLANs allow devices to transmit packets on one VLAN and receive it on another VLAN. This configuration is accomplished
through the use of three functions: enabling Asymmetric VLANs, VLAN creation, and GVRP configuration. Consider the
example below.
Figure 6- 43. Asymmetric VLANs Example
In order to accomplish an Asymmetric VLAN configuration, the user must do a three part configuration:
1. Enable Asymmetric VLANs using the Advanced Settings window located in the Configuration folder. Overlapping
VLANs cannot be configured unless this function is enabled.
2. Configure the VLAN settings. The example above uses ports 1-8 to hold the devices to be shared on the network, such as
shared servers an d shared printers. Therefore, this group of ports is to be in cluded for all VLANs. VLAN V2 is then
configured to include ports 1-8 (shared VLAN ports) and the set of ports to be separated from the other subsetted VLANs
(ports 9-16). VLAN V3 is then configured to include ports 1-8 (shared ports) and the set of ports to be separated from the
other subsetted VLANs (17-24). Therefore we have two VLANs who both share ports and have ports that are separated
from each other and thus cannot communicate with each other.
3. Configure the PVID settings for the Switch through the GVRP function located in the VLANs folder. The user is to set
the shared set of ports as PVID 1, the other separated groups of ports as PVID 2 and PVID 3.
After completing the previous configuration, the user is now able to sh are the network resources set on the shar ed group of ports
(nominated as PVID 1), with both smaller subsets of VLANs (nominated PVID 2 and PVID 3). Yet, VLAN V1 and VLAN V2 are
incapable of sharing information with each other and the Overlapping VLAN configuration has been successfully created.
Page 88
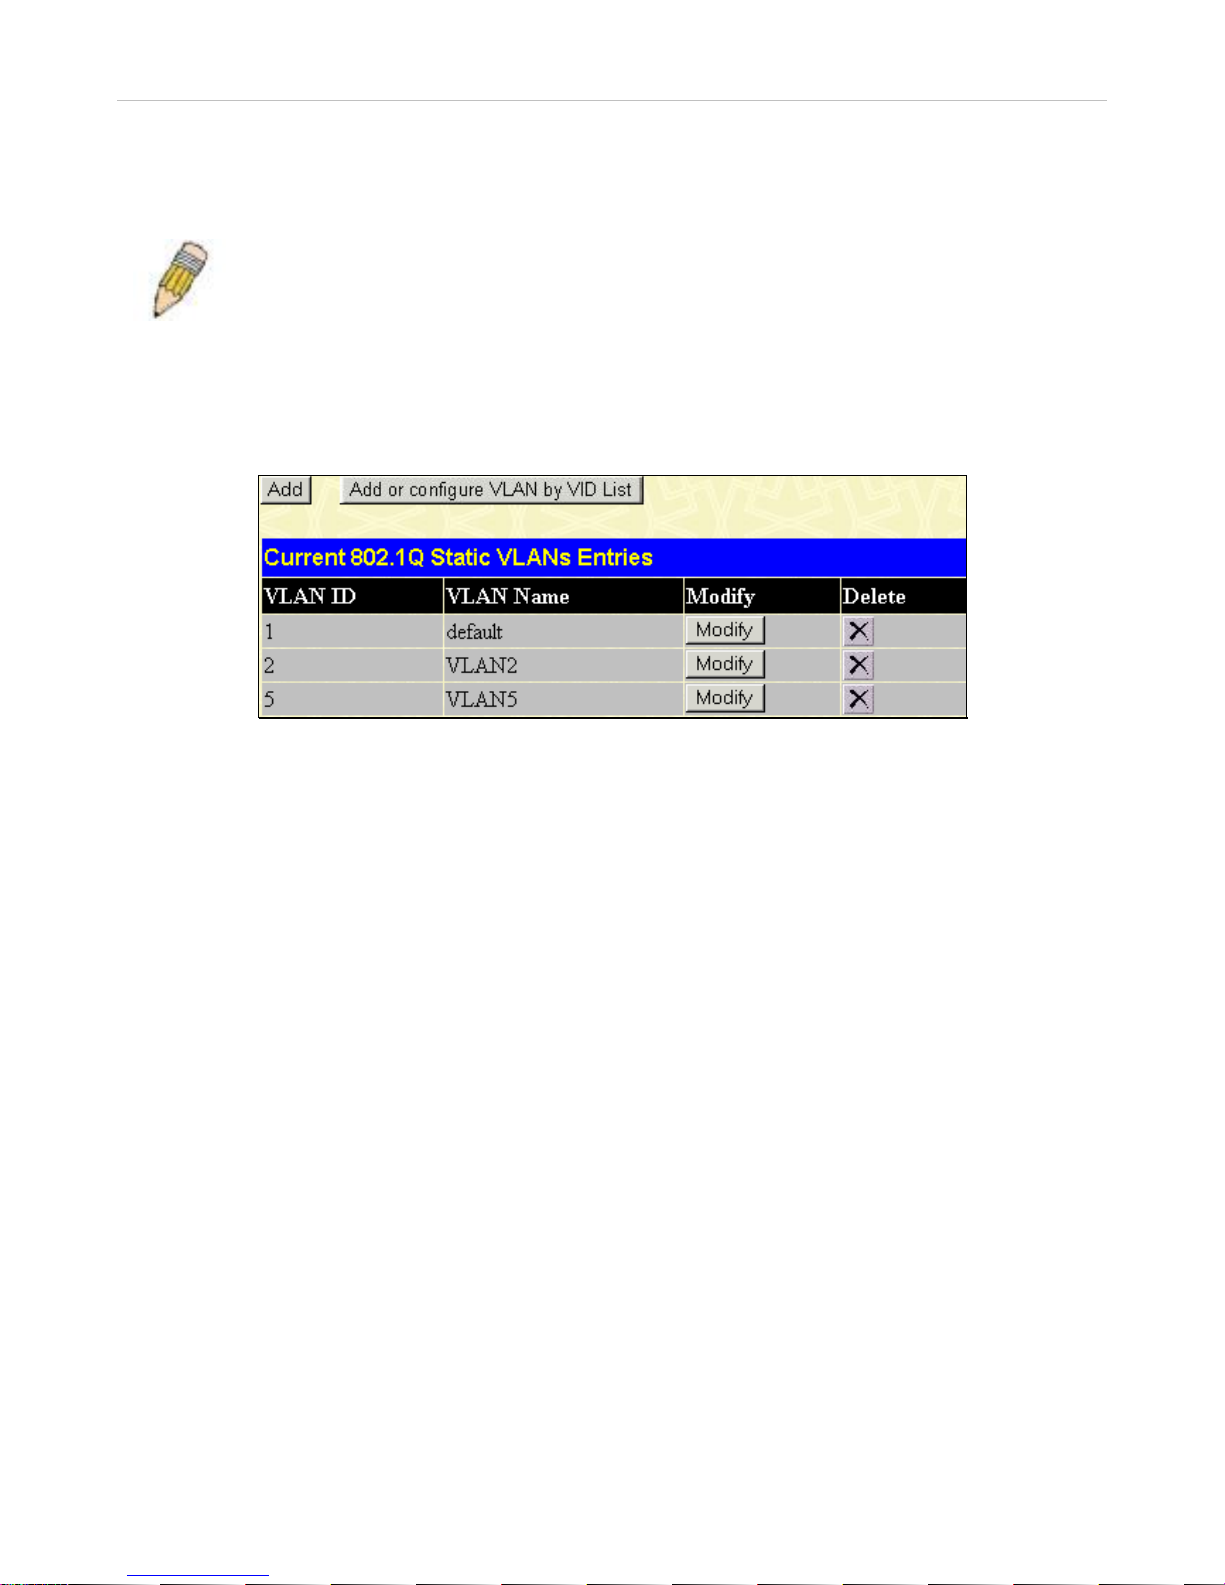
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
73
VLAN and Trunk Groups
The members of a trunk group have the same VLAN setting. Any VLAN setting on the members of a trunk group will apply to
the other member ports.
NOTE: In order to use VLAN segmentation in conjunction with port trunk groups, you can first set
the port trunk group(s), and then you may configure VLAN settings. If you wish to change the port
trunk grouping with VLANs already in place, you will not need to reconfigure the VLAN settings after
changing the port trunk group settings. VLAN settings will automatically change in conjunction with
the change of the port trunk group settings.
Static VLAN Entry
To view the Static VLAN Entries on the Switch click, Configuration > VLAN > Static VLAN Entry wh ich will open the
following window:
Figure 6- 44. Current 802.1Q Static VLANs Entries window
The 802.1Q Static VLANs window lists all previously co nfigured VLANs by VLAN ID and VLAN Name. To delete an existing
802.1Q VLAN, click the corresponding X button under the Delete heading.
To create a new 802.1Q VLAN, click the Add button in the 802.1Q Static VLANs Entries window. A new window will app ear,
as shown below, to configure the port settings and to assign a unique name and number to the new VLAN. See the table below for
a description of the parameters in the new window.
Page 89
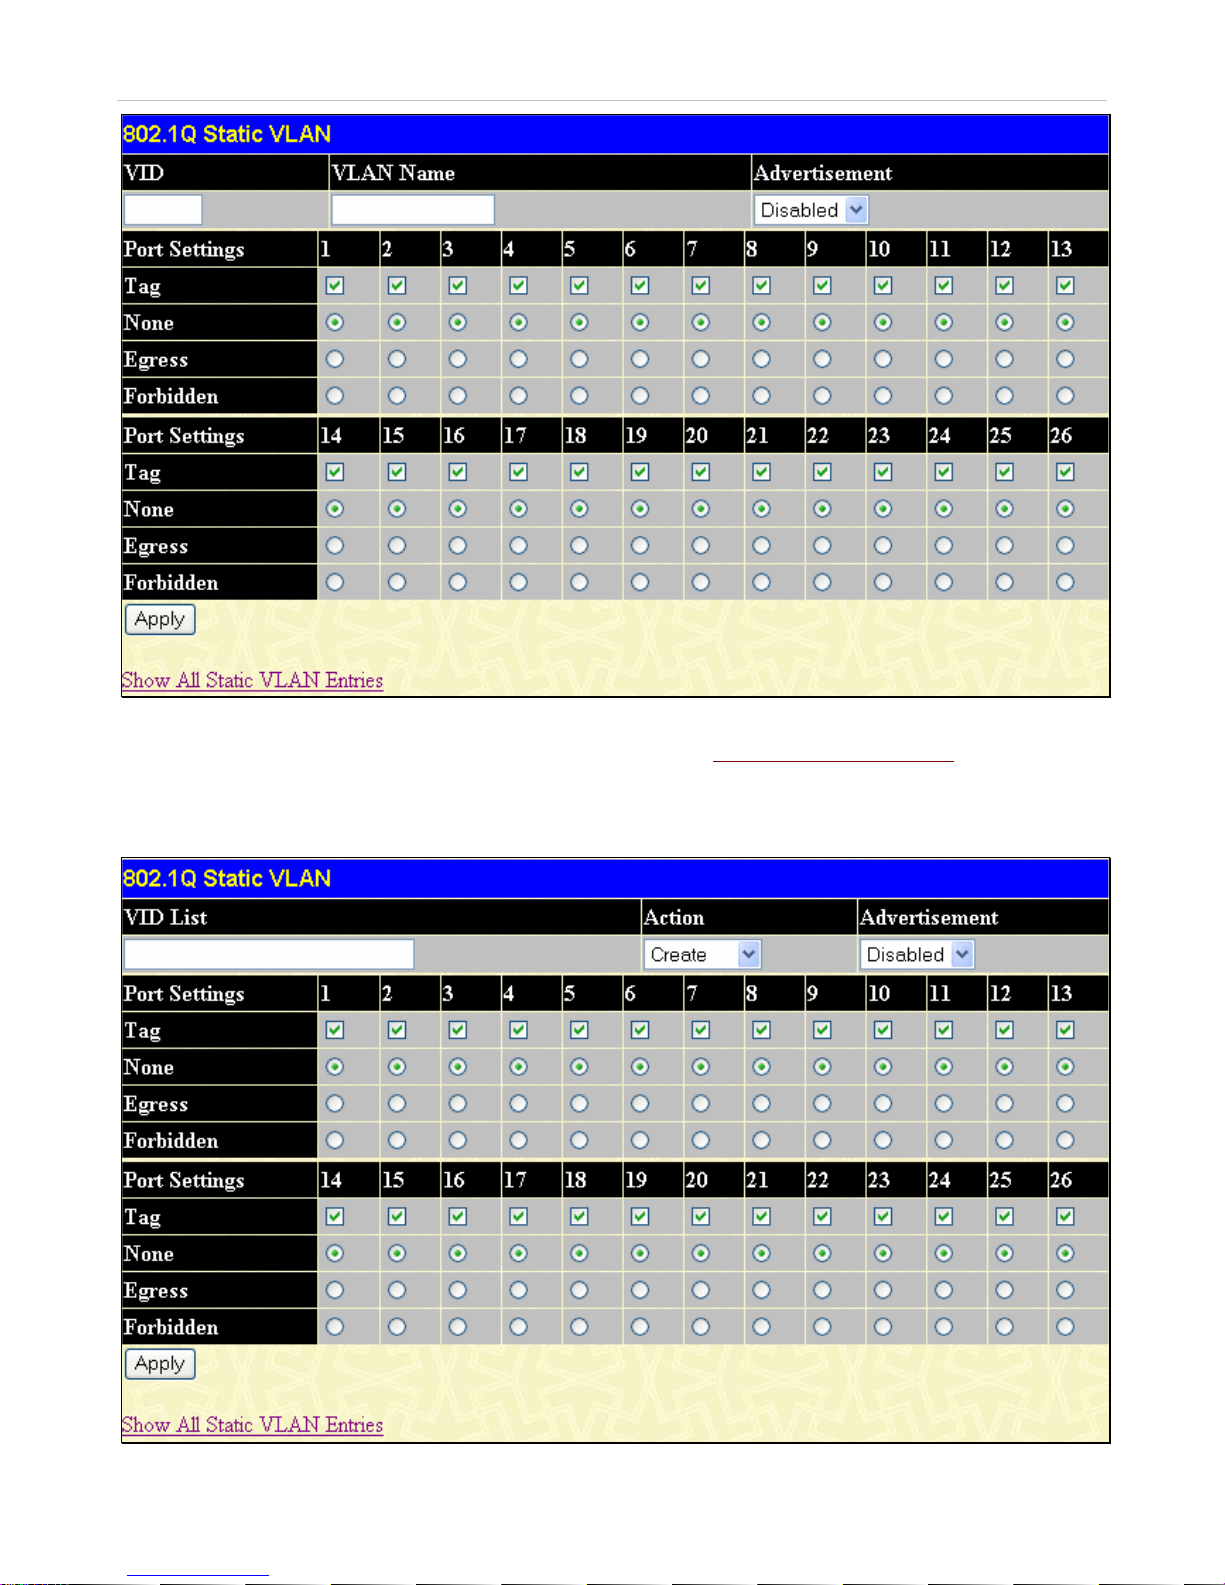
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
74
Figure 6- 45. 802.1Q Static VLAN window - Add
To return to the Current 802.1Q Static VLANs Entries window, click the Show All Static VLAN Entries
link. To change an
existing 802.1Q VLAN entry, click the Modify button of the corresponding entry you wish to modify. A new menu will appear to
configure the port settings and to assign a unique name and number to the new VLAN. See the table below for a description of the
parameters in the new menu. To configure a VLAN by its VID List, click the Add or configure VLAN by VID List button on
the Current 802.1Q Static VLANs Entries table, the following window will appear.
Figure 6- 46. 802.1Q Static VLAN window - Add or configure VLAN by VID List
Page 90
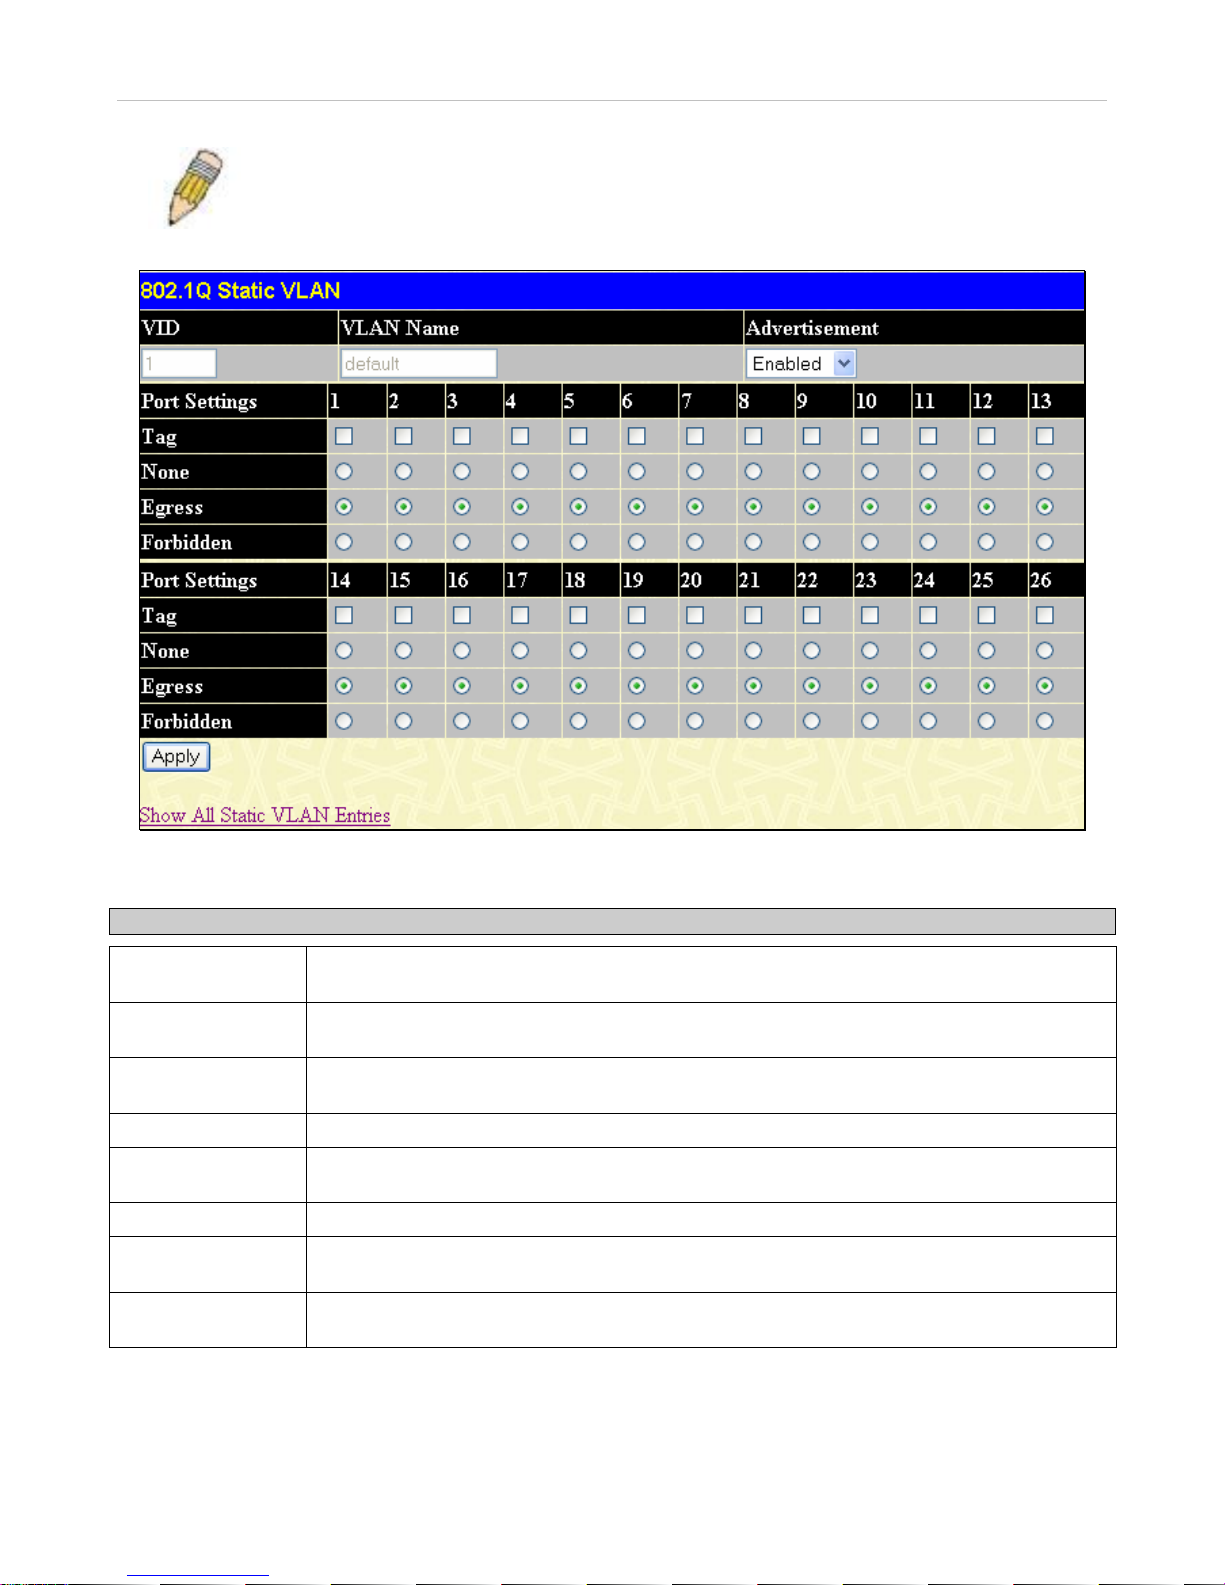
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
75
NOTE: The Switch supports up to 255 static VLAN entries.
Figure 6- 47. 802.1Q Static VLAN window - Modify
The following fields can then be set in either the Add or Modify 802.1Q Static VLANs windows:
Parameter Description
VID (VLAN ID)
Allows the entry of a VLAN ID in the Add window, or displays the VLAN ID of an existing VLAN
in the Modify window. VLANs can be identified by either the VID or the VLAN name.
VLAN Name
Allows the entry of a name for the new VLAN in the Add window, or for editing the VLAN name
in the Modify window.
Advertisement
Enabling this function will allow the Switch to send out GVRP packets to outside sources,
notifying that they may join the existing VLAN.
Port Settings
Allows an individual port to be specified as member of a VLAN.
Tag
Specifies the port as either 802.1Q tagging or 802.1Q untagged. Checking the box will designate the port as Tagged.
None
Allows an individual port to be specified as a non-VLAN member.
Egress
Select this to specify the port as a static member of the VLAN. Egress member ports are ports
that will be transmitting traffic for the VLAN. These ports can be either tagged or untagged.
Forbidden
Select this to specify the port as not being a member of the VLAN and that the port is forbidden
from becoming a member of the VLAN dynamically.
Click Apply to implement changes made.
Page 91
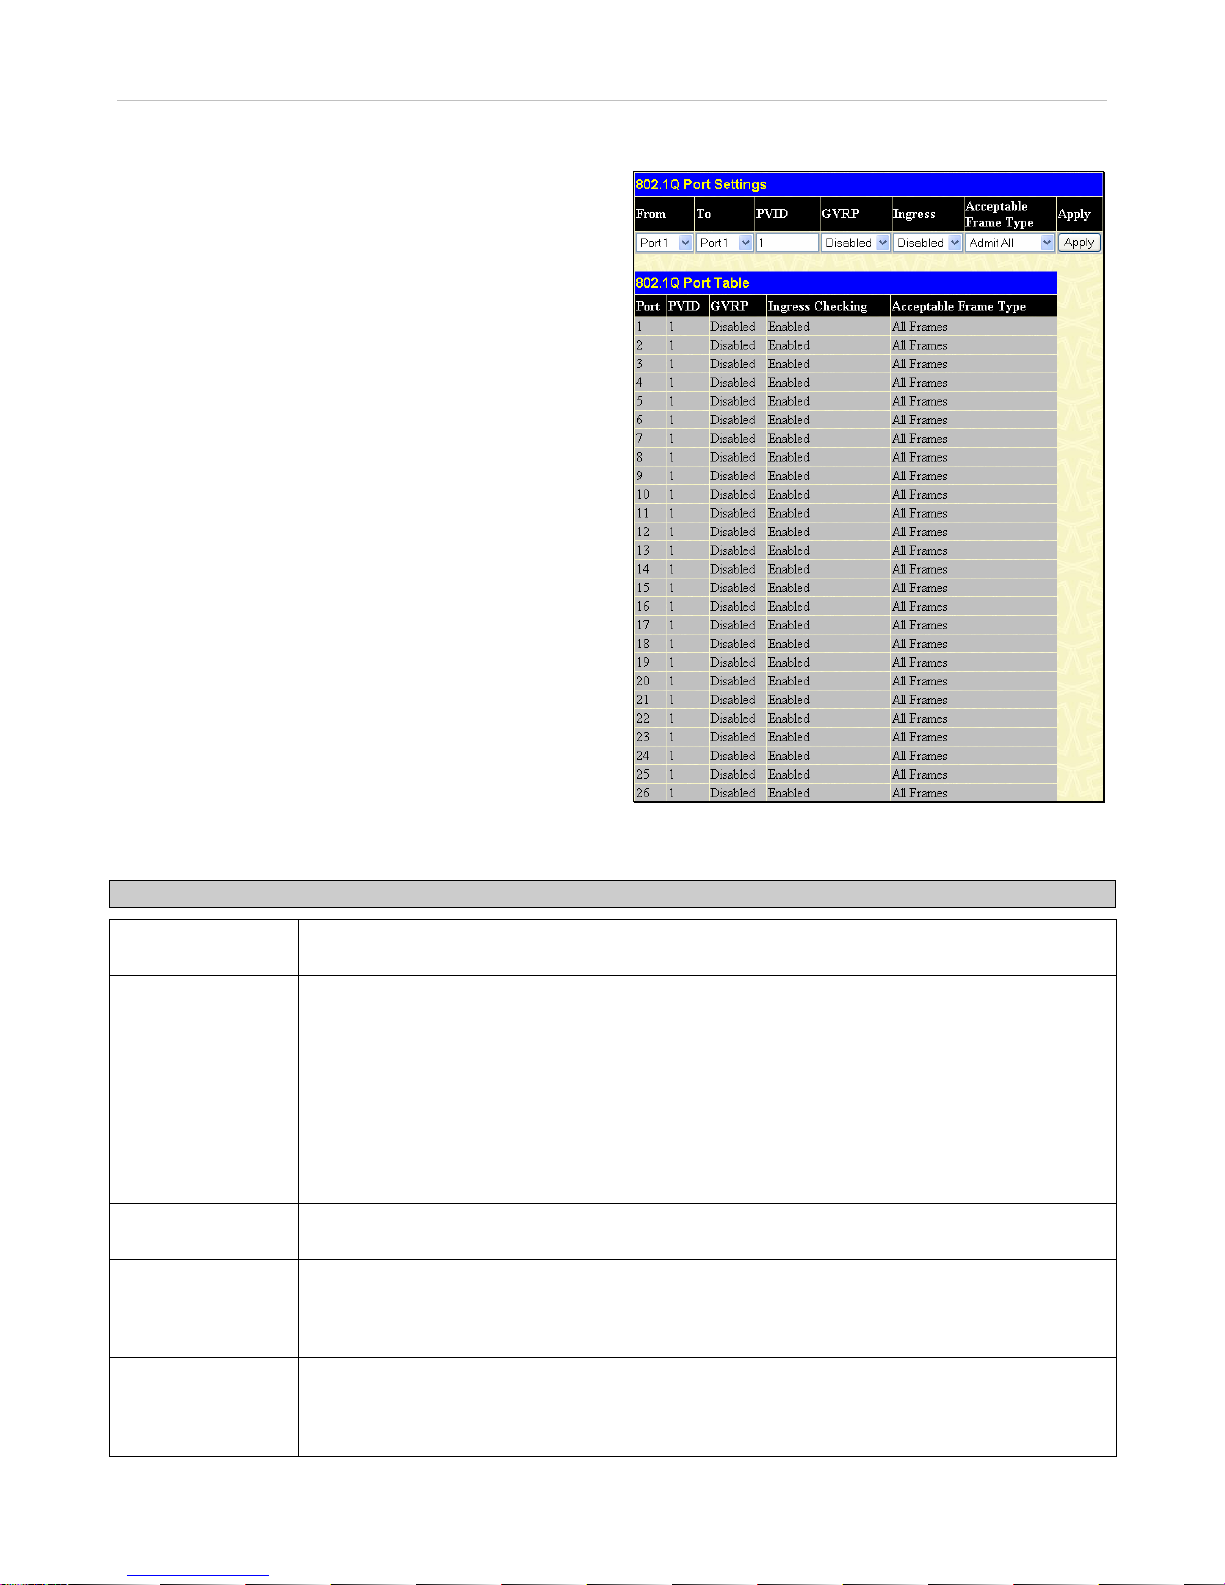
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
76
GVRP Setting
Figure 6- 48. 802.1Q Port Settings window
The following fields can be set:
Parameter Description
From/To
These two fields allow you to specify the range of ports that will be included in the Port-based
VLAN that you are creating using the 802.1Q Port Settings window.
PVID
The read-only field in the 802.1Q Port Table shows the current PVID assignment for each port,
which may be manually assigned to a VLAN when created in the 802.1Q Port Settings table.
The Switch's default is to assign all ports to the default VLAN with a VID of 1.The PVID is used
by the port to tag outgoing, untagged packets, and to make filtering decisions about incoming
packets. If the port is specified to accept only tagged frames - as tagging, and an untagged
packet is forwarded to the port for transmission, the port will add an 802.1Q tag using the PVID
to write the VID in the tag. When the packet arrives at its destination, the receiving device will
use the PVID to make VLAN forwarding decisions. If the port receives a packet, and Ingress
filtering is enabled, the port will compare the VID of the incoming packet to its PVID. If the two
are unequal, the port will drop the packet. If the two are equal, the port will receive the packet.
GVRP
The Group VLAN Registration Protocol (GVRP) enables the port to dynamically become a
member of a VLAN. GVRP is Disabled by default.
Ingress
This field can be toggled using the space bar between Enabled and Disabled. Enabled enables
the port to compare the VID tag of an incoming packet with the PVID number assigned to the
port. If the two are different, the port filters (drops) the packet. Disabled disables ingress filtering. Ingress Checking is Disabled by default.
Acceptable Frame
Type
This field denotes the type of frame that will be accepted by the port. The user may choose
between Tagged Only, which means only VLAN tagged frames will be accepted, and Admit_All,
which mean both tagged and untagged frames will be accepted. Admit_All is enabled by
default.
The 802.1Q Port Settings window, shown below, allows you to
determine whether the Switch will share its VLAN configuration
information with other GARP VLAN Registration Protocol
(GVRP) enabled switches. In addition, Ingress Checking can be
used to limit traffic by filtering incoming packets whose PVID
does not match the PVID of the port. Results can be seen in the
table under the configuration settings, as seen below.
To view this window click, Configuration > VLANs > GVRP
Setting.
Page 92
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
77
Click Apply to implement changes made.
Traffic Control
On a computer network, packets such as Multicast packets and Broadcast packets continually flood the network as normal
procedure. At times, this traffic may increase do to a malicious endstation on the network or a malfunctioning device, such as a
faulty network card. Thus, switch throughput problems will arise and consequently affect the overall performance of the switch
network. To help rectify this packet storm, the Switch will monitor and control the situation.
The packet storm is monitored to determine if too many packets are flooding the network, based on the threshold level provided
by the user. Once a packet storm has been detected, the Switch will drop packets coming into the Switch until the storm has
subsided. This method can be utilized by selecting the Drop option of the Action field in the window below.
The Switch will also scan and monitor packets coming into the Switch by monitoring the Switch’s chip counter. This method is
only viable for Broadcast and Multicast storms because the chip only has counters for these two types of packets. Once a storm
has been detected (that is, once the packet threshold set below has been exceeded), the Switch will shutdown the port to all
incoming traffic with the exception of STP BPDU packets, for a time period specified using the CountDown field. If this field
times out and the packet storm continues, the port will be placed in a Shutdown Forever mode which will produce a warning
message to be sent to the Trap Receiver. Once in Shutdown Forever mode, one method of recovering this port is to manually
recoup it using the Port Configuration window in the Configuration folder, and selecting the disabled port and returning it to an
Enabled status. Otherwise, the Shutdown Forever mode will be Auto-Recovery after 5 mins. To utilize this method of Storm
Control, choose the Shutdown option of the Action field in the window below. To view this window click, Configuration >
Traffic Control.
Page 93
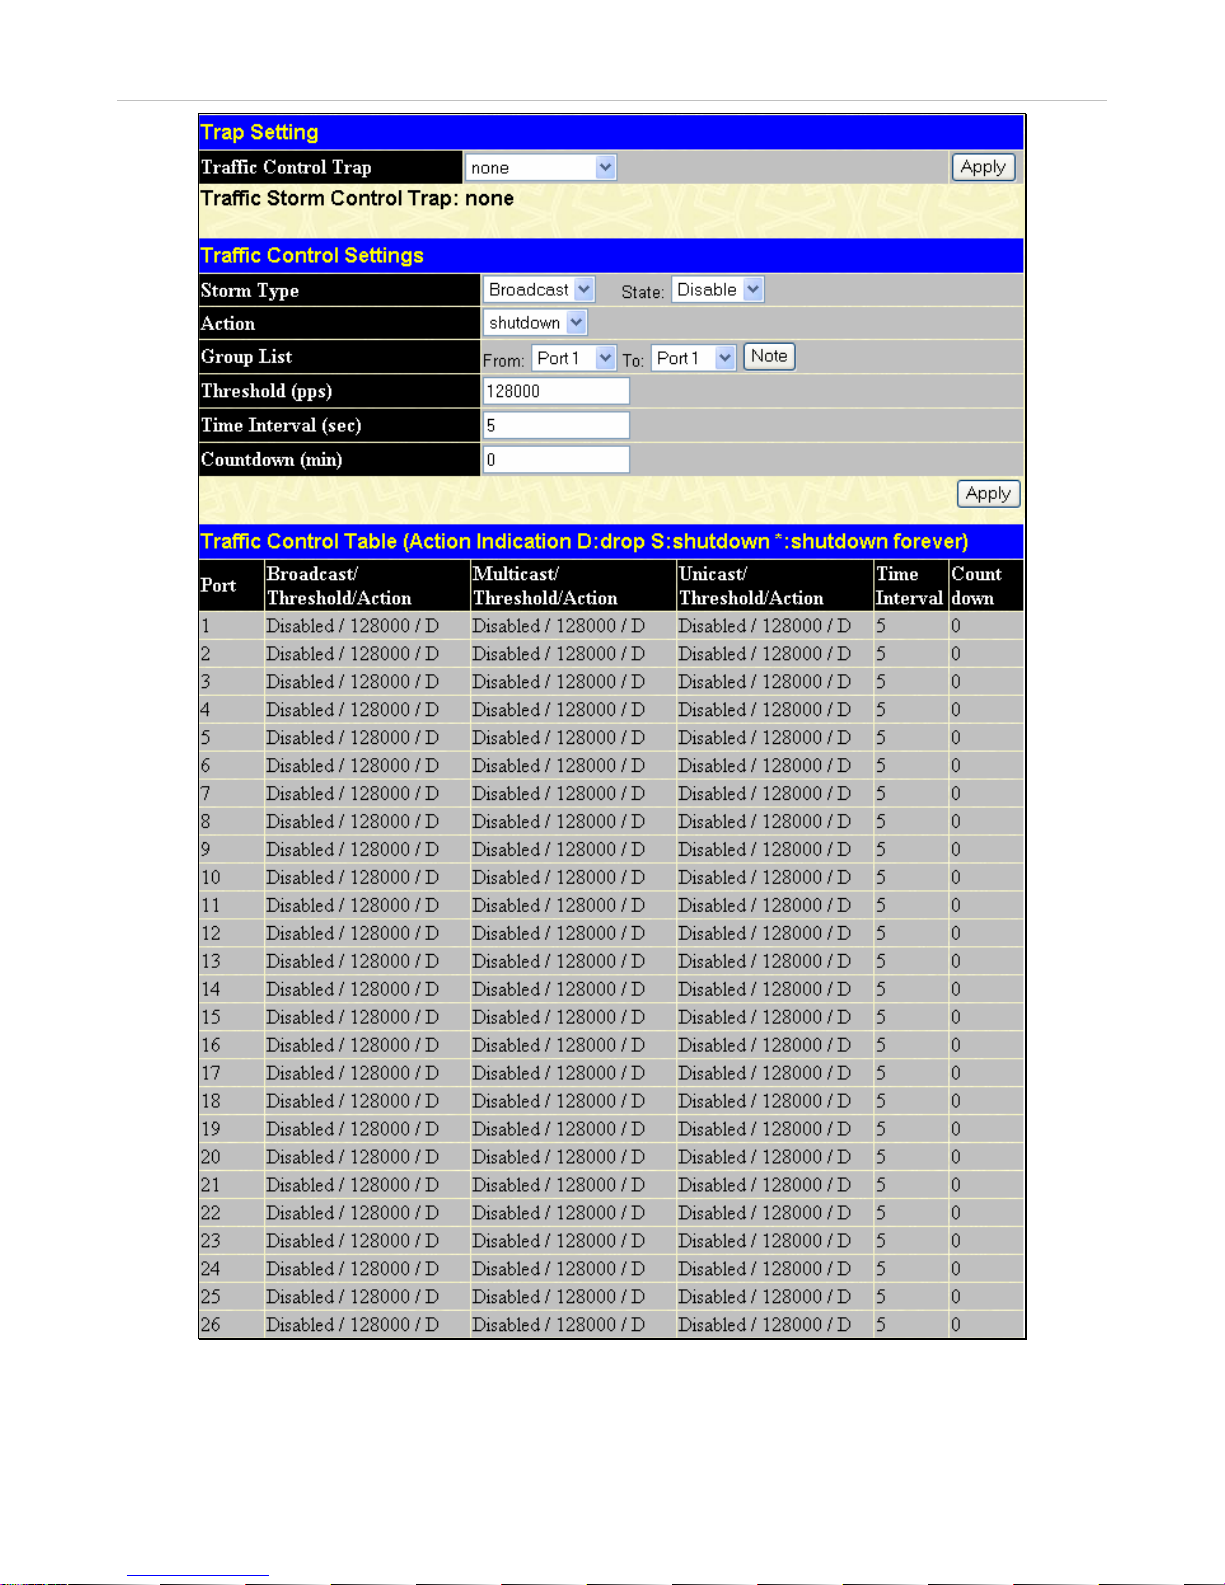
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
78
Figure 6- 49. Traffic Control Setting window
Page 94
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
79
Use the Traffic Control Setting window to enable or disable storm control and adjust the threshold for multicast and broadcast
storms, as well as Unicast (Destination Look Up Failure). Traffic control settings are applied to individual Switch modules. To
view the following window, click Configuration > Traffic Control:
The user may set the following parameters:
Parameter Description
Trap Setting
Traffic Control
Trap
Enable sending of Storm Trap messages when the type of action taken by the Traffic Control
function in handling a Traffic Storm is one of the following:
None – Will send no Storm trap warning messages regardless of action taken by the Traffic
Control mechanism.
Storm Occurred – Will send Storm Trap warning messages upon the occurrence of a Traffic
Storm only.
Storm Cleared – Will send Storm Trap messages when a Traffic Storm has been cleared by the
Switch only.
Both – Will send Storm Trap messages when a Traffic Storm has been both detected and
cleared by the Switch.
This function cannot be implemented in the Hardware mode. (When Drop is chosen in the Action
field.
Traffic Control Settings
Storm Type
Select the type of Storm Type to detect, either Broadcast Multicast or Unicast. Once selected , use
the pull-down menu to enable or disable this storm detection.
Action
Select the method of traffic Control from the pull down menu. The choices are:
shutdown – Utilizes the Switch’s software Traffic Control mechanism to determine the Packet Storm
occurring. Once detected, the port will deny all incoming traffic to the port except STP BPDU
packets, which are essential in keeping the Spanning Tree operational on the Switch. If the
countdown timer has expired and yet the Packet Storm continues, the port will be placed in
Shutdown Forever mode and is no longer operational until the user manually resets the port using
the config ports enable command or waits for 5 mins to let the Shutdown Forever mode enter AutoRecovery. Choosing this option obligates the user to configure the Interval setting as well, which will
provide packet count samplings from the Switch’s chip to determine if a Packet Storm is occurring.
drop – Utilizes the hardware Traffic Control mechanism, which means the Switch’s hardware will
determine the Packet Storm based on the Threshold value stated and drop packets until the issue is
resolved.
Group List
Select the ports to be manually recovered from the Shutdown state.
Threshold
Specifies the maximum number of packets per second that will trigger the Traffic Control function to
commence. The configurable threshold range is from 0-255000 with a default setting of 128000.
Time Interval
The Interval will set the time between Multicast and Broadcast packet counts sent from the Switch’s
chip to the Traffic Control function. These packet counts are the determining factor in deciding when
incoming packets exceed the Threshold value. The Interval may be set between 5 and 30 seconds
with the default setting of 5 seconds.
Count Down
The Count Down timer is set to determine the amount of time, in minutes, that the Switch will wait
before shutting down the port that is experiencing a traffic storm. This parameter is only useful for
ports configured as Shutdown in their Action field and therefore will not operate for Hardware based
Traffic Control implementations. The possible time settings for this field are 0, 5-30 minutes. 0 is the
default setting for this field and 0 will denote that the port will immediately shutdown.
Click Apply to implement the settings made.
NOTE: Traffic Control cannot be implemented on ports that are set for Link Aggregation (Port Trunking).
Page 95
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
80
NOTE: Ports that are in the Shutdown forever mode will be seen as Discarding in Spanning Tree
windows and implementations though these ports will still be forwarding BPDUs to the Switch’s CPU.
NOTE: Ports that are in Shutdown Forever mode will be seen as link down in all windows and screens
until the user recovers these ports or waits for 5 mins to let the Shutdown Forever mode enter AutoRecovery.
NOTE: When configuring the traffic storm settings, remember that when it is configured for shutdown,
the Group List will refer to individual ports. Yet, when the traffic control is configured for drop, the group
list refers to groups of ports. (Ex – 1 refers to ports 1 through 8, 2 refers to ports 9-16…)
The group list settings for drop are as follows:
Group 1 - Inclusive for ports 1-8.
Group 2 - Inclusive for ports 9-16.
Group 3 - Inclusive for ports 17-24.
Group 4 - Inclusive for ports 9-16 (DES-3550). Inclusive for Gigabit port 25 (DES-3526).
Group 5 - Inclusive for ports 33-40 (DES-3550). Inclusive for Gigabit port 26 (DES-3526).
Group 6 - Inclusive for ports 41-48 (DES-3550 only).
Group 7 - Inclusive for Gigabit port 49 (DES-3550 only).
Group 8 - Inclusive for Gigabit port 50 (DES-3550 only).
Page 96
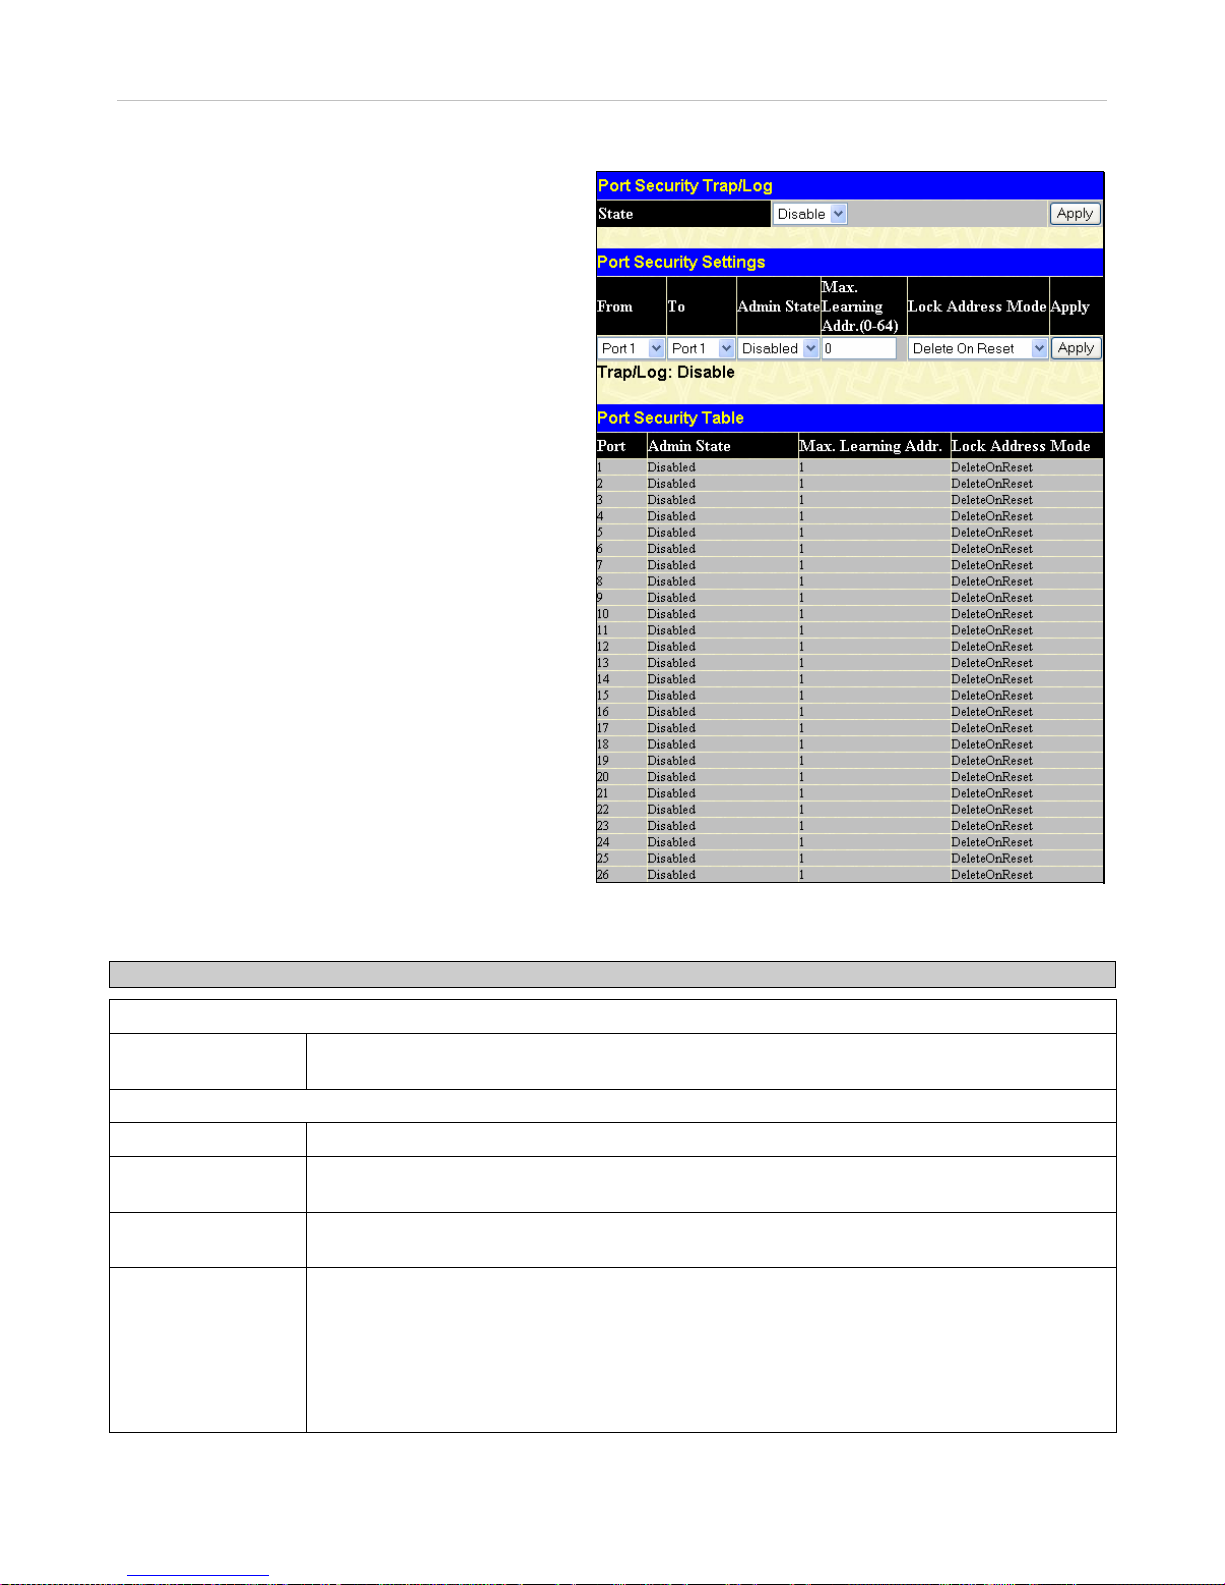
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
81
Port Security
Figure 6- 50. Port Security Settings window
The following parameters can be set:
Parameter Description
Port Security Trap/Log
State
Use the pull-down menu the enable or disable Port Security Trap/Log messages to be sent to
the Switch’s log file and to the SNMP manager.
Port Security Settings
From/To
A consecutive group of ports may be configured starting with the selected port.
Admin State
This pull-down menu allows you to enable or disable Port Security (locked MAC address table
for the selected ports).
Max. Learning
Addr. (0-64)
The number of MAC addresses that will be in the MAC address-forwarding table for the
selected switch and group of ports.
Lock Address
Mode
This pull-down menu allows you to select how the MAC address table locking will be
implemented on the Switch, for the selected group of ports. The options are:
• Permanent – The locked addresses will not age out after the aging timer expires.
• Delete OnTimeout – The locked addresses will age out after the aging timer expires.
• Delete On Reset – The locked addresses will not age out until the Switch has been
reset.
Click Apply to implement changes made.
A given port's (or a range of ports') dynamic MAC address
learning can be locked such that the current source MAC
addresses entered into the MAC address forwarding table
can not be changed once the port lock is enabled. Using the
Admin State pull-down menu to Enabled, and clicking
Apply can lock the port.
Port Security is a security feature that prevents unauthorized
computers (with source MAC addresses) unknown to the
Switch prior to locking the port (or ports) from connecting
to the Switch's locked ports and gaining access to the
network. To view this window click, Configuration > Port
Security.
Page 97
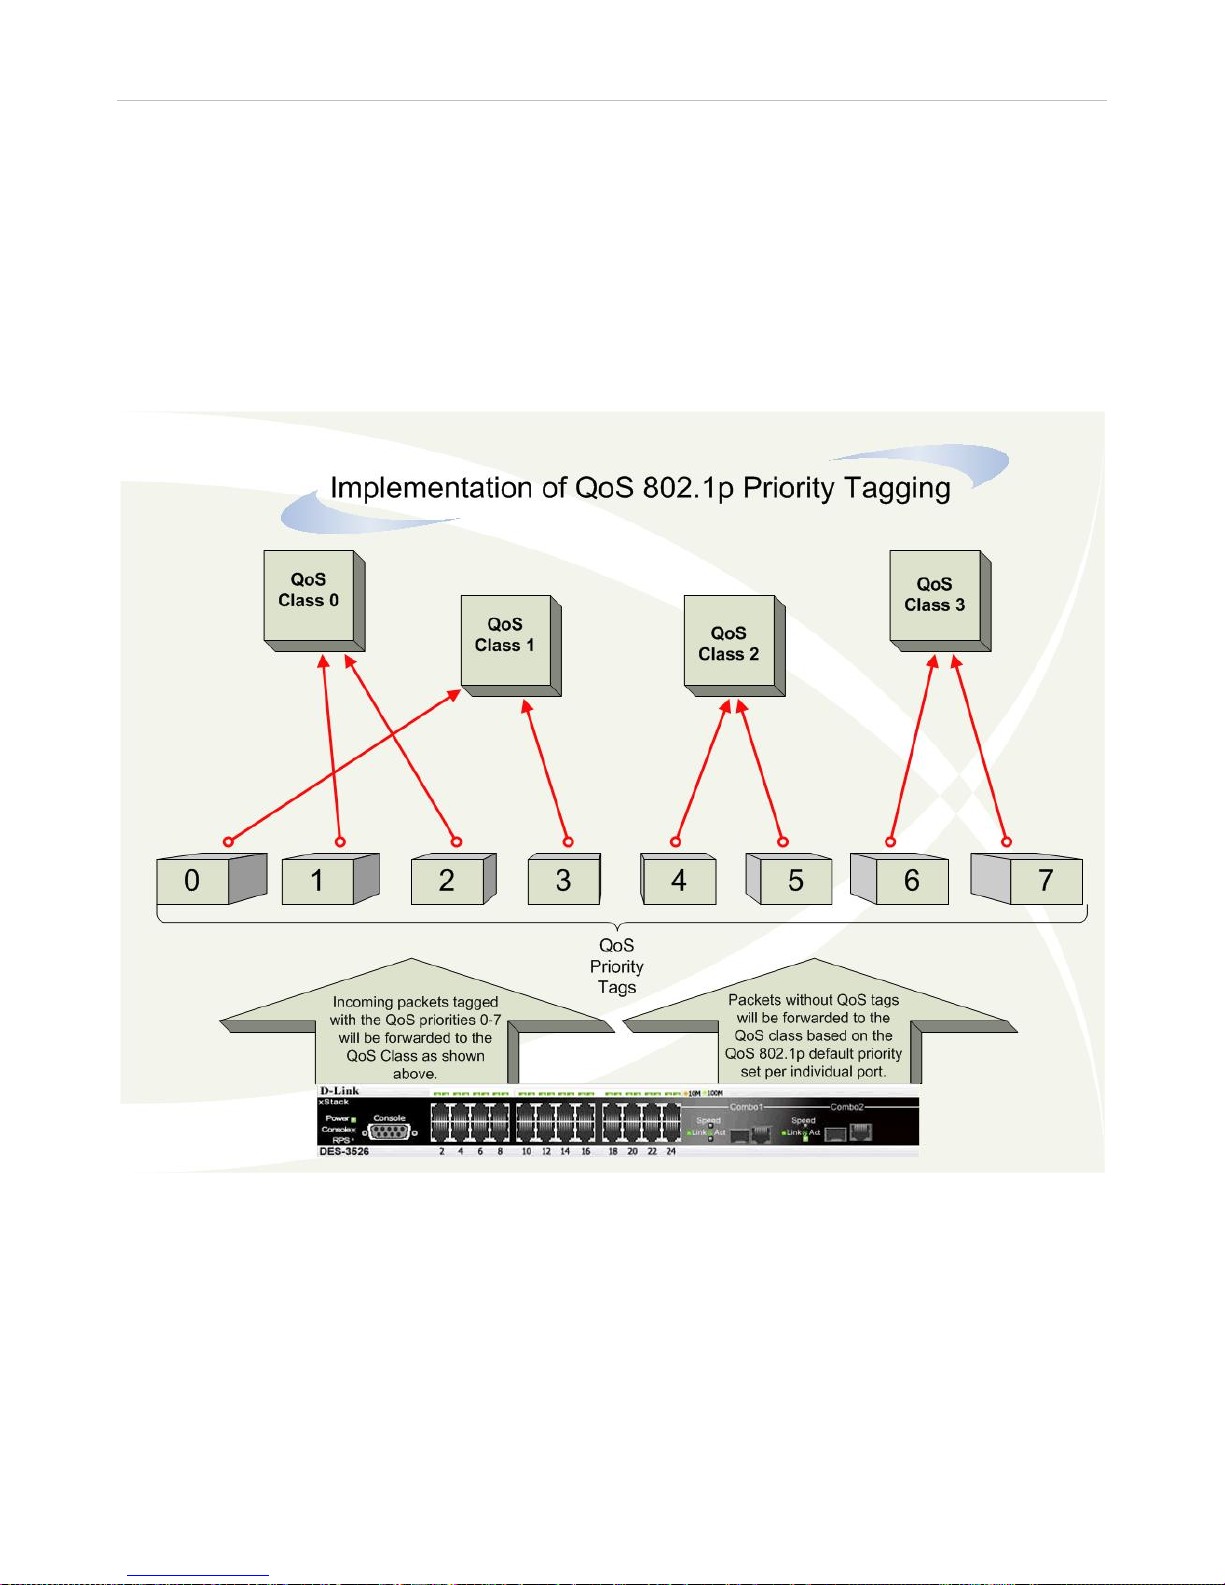
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
82
QoS
The DES-3500 Series switches supports 802.1p priority queuing Quality of Service. The following section discusses the
implementation of QoS (Quality of Service) and benefits of using 802.1p priority queuing.
Advantages of QoS
QoS is an implementation of the IEEE 802.1p standard that allows network administrators a method of reserving bandwidth for
important functions that require a large bandwidth or have a high priority, such as VoIP (voice-over Internet Protocol), web
browsing applications, file server applications or video conferencing. Not only can a larger bandwidth be created, but other less
critical traffic can be limited, so excessive bandwidth can be saved. The Switch has separate hardware queues on every physical
port to which packets from various applications can be mapped to, and, in turn prioritized. View the following map to see how the
DES-3500 Series switches implements 802.1P priority queuing.
Figure 6- 51. Mapping QoS on the Switch
The picture above shows the default priority setting for the Switch. Class-3 ha s the highest priority of the four p riority queues on
the Switch. In order to implement QoS, the user is required to instruct the Switch to examine the header of a packet to see if it has
the proper identifying tag tagged. Then the user may forward these tagged pack ets to desig na ted que ues on the Switch where they
will be emptied, based on priority.
For example, lets say a user wishes to have a video conference between two remotely set computers. The administrator can add
priority tags to the video packets being sent out, utilizing the Access Profile commands. Then, on the receiving end, the
administrator instructs the Switch to examine packets for this tag, acquires the tagged packets and maps them to a class queue on
the Switch. Then in turn, the administrator will set a priority for this queue so that will be emptied before any other packet is
forwarded. This results in the end user receiving all packets sent as quickly as possible, thus prioritizing the queue and allowing
for an uninterrupted stream of packets, which optimizes the use of bandwidth available for the video conference.
Page 98
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
83
Understanding QoS
The Switch has four priority queues. These priority queues are labeled as 3, the high queue to 0, the lowest queue. The eight
priority tags, specified in IEEE 802.1p are mapped to the Switch's priority tags as follows:
• Priority 0 is assigned to the Switch's Q1 queue.
• Priority 1 is assigned to the Switch's Q0 queue.
• Priority 2 is assigned to the Switch's Q0 queue.
• Priority 3 is assigned to the Switch's Q1 queue.
• Priority 4 is assigned to the Switch's Q2 queue.
• Priority 5 is assigned to the Switch's Q2 queue.
• Priority 6 is assigned to the Switch's Q3 queue.
• Priority 7 is assigned to the Switch's Q3 queue.
For strict priority-based scheduling, any packets residing in the higher priority queues are transmitted first. Multiple strict priority
queues empty based on their priority tags. Only when these queues are empty, are packets of lower priority transmitted.
For weighted round robin queuing, the number of packets sent from each priority queue depends upon the assigned weight. For a
configuration of 8 CoS queues, A~H with their respective weight value: 8~1, the packets are sent in the following sequence: A1,
B1, C1, D1, E1, F1, G1, H1, A2, B2, C2, D2, E2, F2, G2, A3, B3, C3, D3, E3, F3, A4, B4, C4, D4, E4, A5, B5, C5, D5, A6, B6,
C6, A7, B7, A8, A1, B1, C1, D1, E1, F1, G1, H1.
For weighted round robin queuing, if each CoS queue has the same weight value, then each CoS queue has an equal opportunity to
send packets just like round robin queuing.
For weighted round-robin queuing, if the weight for a CoS is set to 0, then it will continue processing the packets from this CoS
until there are no more packets for this CoS. The other CoS queues that have been given a nonzero value, and depending upon the
weight, will follow a common weighted round-robin scheme.
Remember that the DES-3500 Series switches has four priority queues (and four Classes of Service) for each port on the Switch.
Page 99
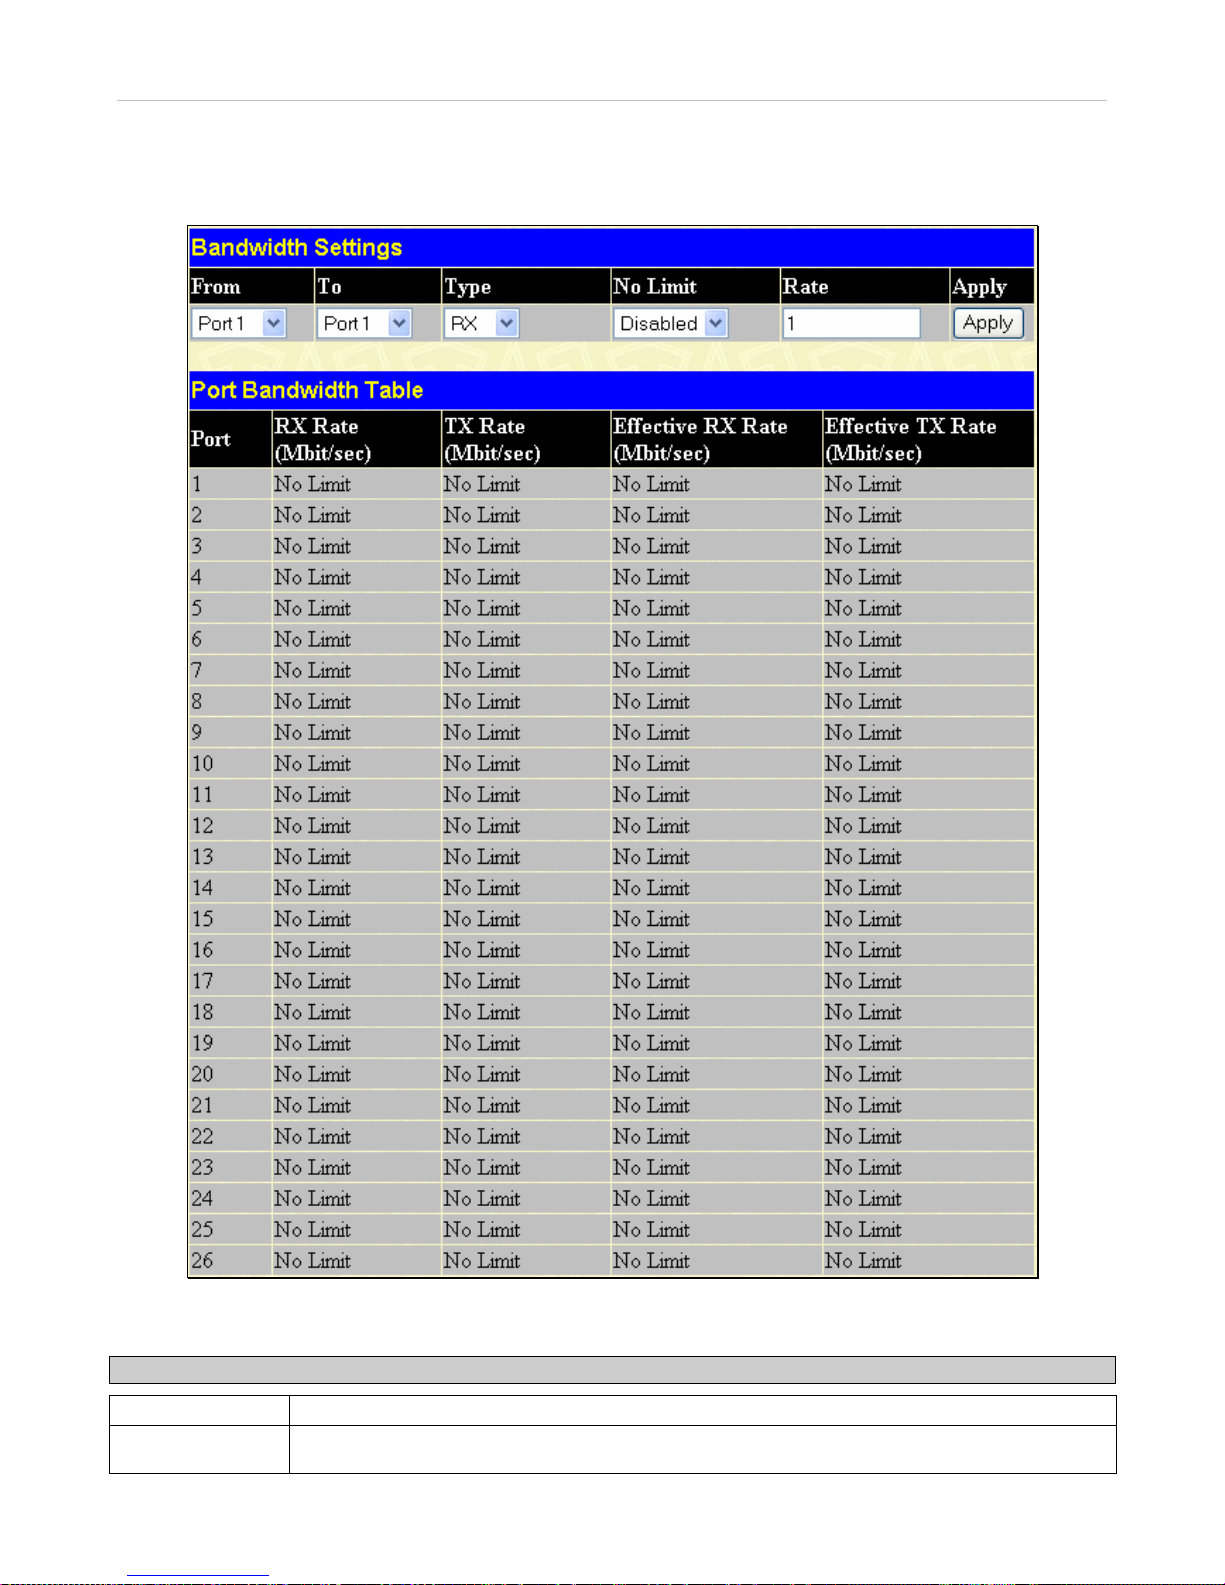
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
84
Port Bandwidth
The bandwidth control settings are used to place a ceiling on the transmitting and receiving data rates for any selected port. Click
Configuration > QoS > Port Bandwidth, to view the window shown below.
Figure 6- 52. Bandwidth Settings window
The following parameters can be set or are displayed:
Parameter Description
From/To
A consecutive group of ports may be configured starting with the selected port.
Type
This drop-down menu allows you to select between RX (receive), TX (transmit), and Both. This
setting will determine whether the bandwidth ceiling is applied to receiving, transmitting, or both
Page 100
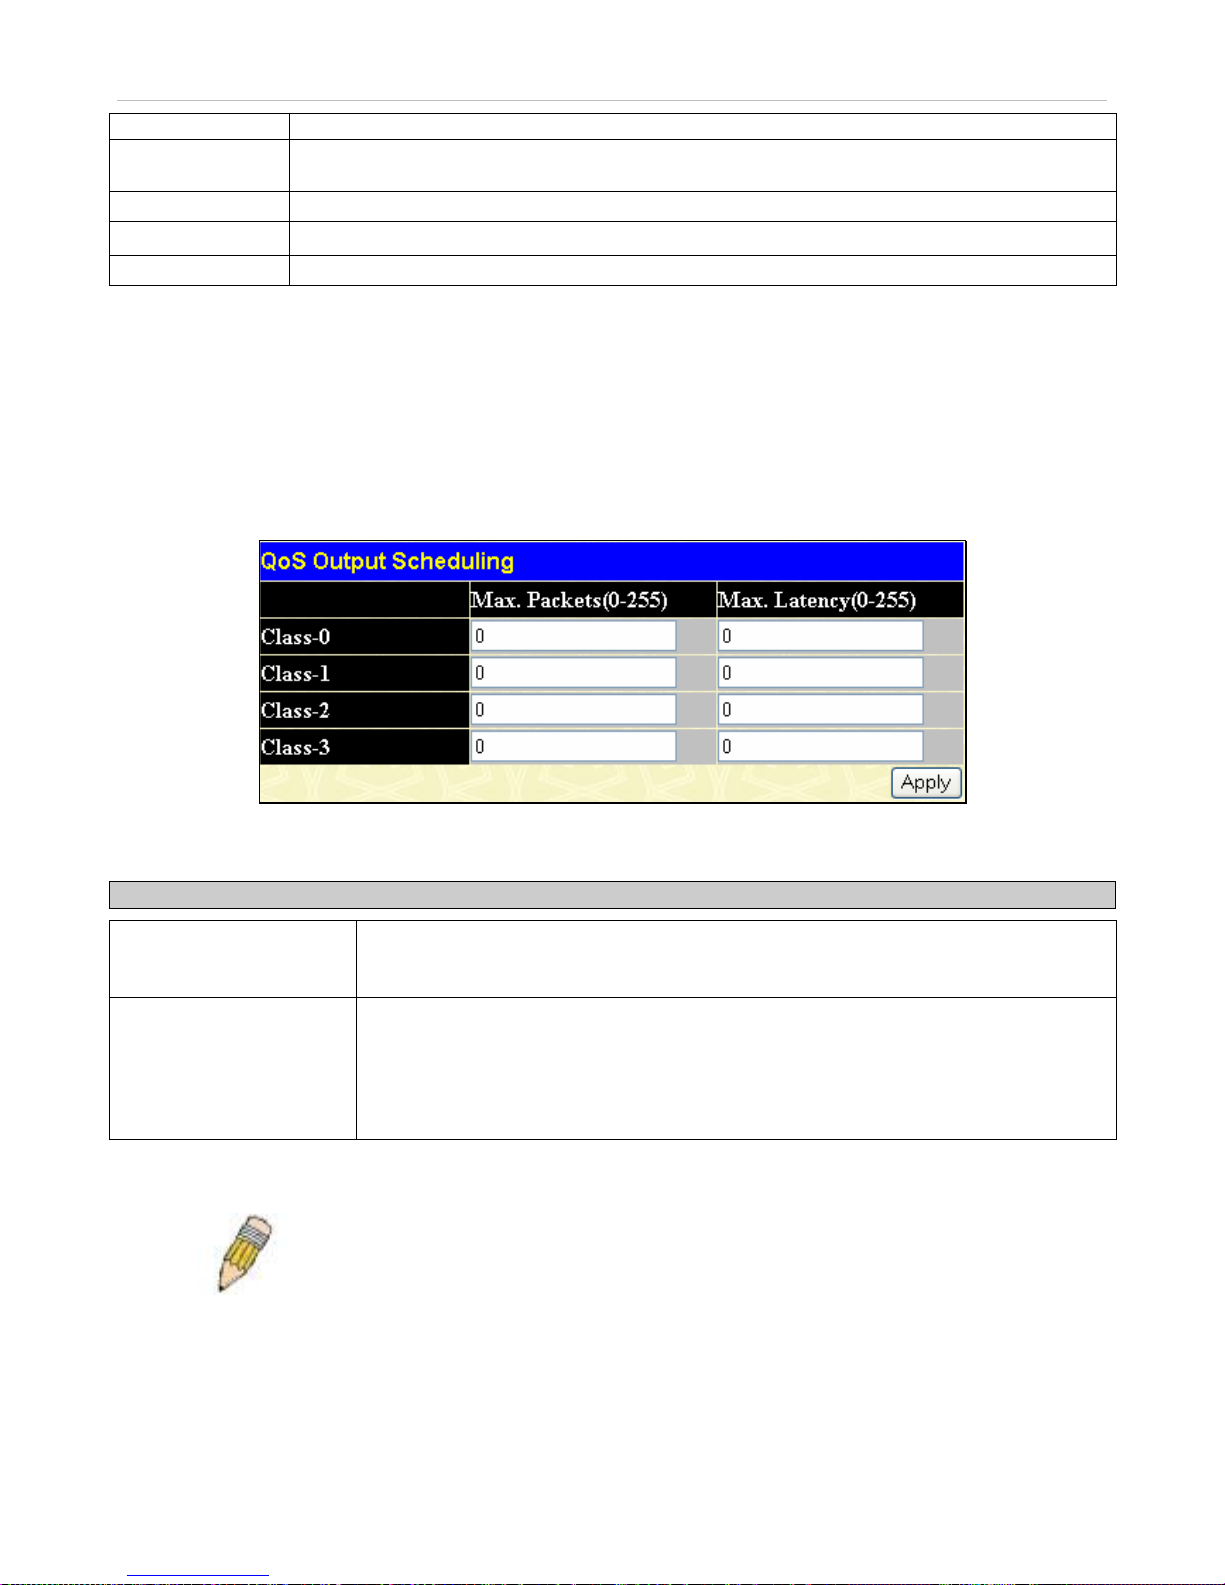
xStack® DES-3500 Series Layer 2 Stackable Fast Ethernet Managed Switch User Manual
85
receiving and transmitting packets.
No Limit
This drop-down menu allows you to specify that the selected port will have no bandwidth limit.
Enabled disables the limit.
Rate
This field allows you to enter the data rate, in Mbit/s, that will be the limit for the selected port.
Effective Rx rate
Specifies the limitation of the received data rate.
Effective Tx rate
Specifies the limitation of the transmitted data rate.
Click Apply to set the bandwidth control for the selected ports. Results of configured Bandwidth Settings will be displayed in th e
Port Bandwidth Table.
Scheduling
Changing the output scheduling used for the hardware queues in the Switch can customize QoS. As with any changes to QoS
implementation, careful consideration should be given to how network traffic in lower priority queues is affected. Changes in
scheduling may result in unacceptable levels of packet loss or significant transmission delay. If you choose to customize this
setting, it is important to monitor network performance, especially during peak demand, as bottlenecks can quickly deve lop if the
QoS settings are not suitable. Click, Configuration > QoS > Scheduling to view the window shown below.
Figure 6- 53. QoS Output Scheduling window
You may assign the following values to the QoS classes to set the scheduling.
Parameter Description
Max. Packets (0-255)
Specifies the maximum number of packets the above specified hardware priority queue
would be allowed to transmit before allowing the next lowest priority queue to transmit its
packets. A value between 0 and 255 can be specified.
Max. Latency (0-255)
Specifies the maximum amount of time the above specified hardware priority queue will
be allowed to transmit packets before allowing the next lowest hardware priority queue to
begin transmitting its packets. A value between 0 and 255 can be specified - with this
value multiplied by 16 ms to arrive at the total allowed time for the queue to transmit
packets. For example, a value of 3 specifies 3 X 16 = 48 ms. The queue will continue
transmitting the last packet until it is finished when the max latency timer expires.
Click Apply to implement changes made.
NOTE: The settings you assign to the queues, numbers 0-7, represent the IEEE
802.1p priority tag number. Do not confuse these settings with port numbers.
 Loading...