

Page 1
Page 2
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Table of Contents
Chapter 1 Using the Command Line Interface............................................................................. 1
Chapter 2 Basic Management Commands .................................................................................. 9
Chapter 3 802.1X Commands.................................................................................................... 32
Chapter 4 Access Authentication Control (AAC) Commands .................................................... 57
Chapter 5 Access Control List (ACL) Commands.................................................................... 100
Chapter 6 Access Control List (ACL) Egress Commands ....................................................... 128
Chapter 7 ARP Commands...................................................................................................... 147
Chapter 8 ARP Spoofing Prevention Commands .................................................................... 154
Chapter 9 Asymmetric VLAN Commands ................................................................................ 156
Chapter 10 Auto Configuration Commands ............................................................................... 158
Chapter 11 Bidirectional Forwarding Detection (BFD) Commands ........................................... 160
Chapter 12 Border Gateway Protocol (BGP) Commands ......................................................... 165
Chapter 13 BPDU Attack Protection Commands....................................................................... 224
Chapter 14 Cable Diagnostics Commands ................................................................................ 229
Chapter 15 CFM Commands ..................................................................................................... 232
Chapter 16 Command List History Commands ......................................................................... 268
Chapter 17 Command Logging Commands .............................................................................. 271
Chapter 18 Common Unicast Routing Commands .................................................................... 273
Chapter 19 Compound Authentication Commands ................................................................... 287
Chapter 20 Debug Software Commands ................................................................................... 297
Chapter 21 DHCP Local Relay Commands ............................................................................... 368
Chapter 22 DHCP Relay Commands ........................................................................................ 372
Chapter 23 DHCP Server Commands ....................................................................................... 390
Chapter 24 DHCP Server Screening Com mands ...................................................................... 413
Chapter 25 DHCPv6 Relay Commands ..................................................................................... 425
Chapter 26 DHCPv6 Server Commands ................................................................................... 432
Chapter 27 Digital Diagnostic Monitoring (DDM) Commands ................................................... 447
Chapter 28 Distance Vector Multicast Rout ing Prot oc ol (DVMRP) Commands ........................ 454
Chapter 29 D-Link License Management System (DLMS) Commands .................................... 460
Chapter 30 Domain Name System (DNS) Relay Commands ................................................... 462
Chapter 31 Domain Name System (DNS) Resolver Commands .............................................. 467
Chapter 32 DoS Attack Prevention Commands......................................................................... 474
Chapter 33 D-Link Unidirectional Link Detection (DULD) Commands ...................................... 478
Chapter 34 Ethernet Ring Protection Switching (ERPS) Commands ........................................ 480
Chapter 35 Energy Efficient Ethernet (EEE) Commands .......................................................... 489
Chapter 36 External Alarm Commands ..................................................................................... 491
Chapter 37 FDB Commands ...................................................................................................... 493
II
Page 3
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Chapter 38
Chapter 39 Filter Commands ..................................................................................................... 512
Chapter 40 FTP Client Commands ............................................................................................ 515
Chapter 41 Gratuitous ARP Commands .................................................................................... 523
Chapter 42 Internet Group Management Protocol (IGMP) Commands..................................... 528
Chapter 43 IGMP Proxy Commands ......................................................................................... 536
Chapter 44 IGMP Snooping Commands ................................................................................... 541
Chapter 45 IGMP Snooping Multicast (ISM) VLA N Commands ................................................ 560
Chapter 46 IP Interface Commands .......................................................................................... 571
Chapter 47 IP Multicasting Commands ..................................................................................... 581
Chapter 48 IP Route Filter Commands ...................................................................................... 586
Chapter 49 IP Routing Commands ............................................................................................ 605
Chapter 50 IP Tunnel Commands ............................................................................................. 618
Chapter 51 IPv6 NDP Commands ............................................................................................. 628
Chapter 52 IP-MAC-Port Binding (IMPB) Commands ............................................................... 636
Chapter 53 Japanese Web-based Access Control (JWAC) Commands ................................... 666
Chapter 54 Jumbo Frame Commands ....................................................................................... 690
File System Management Commands .................................................................... 502
Chapter 55 LACP Configuration Commands ............................................................................. 693
Chapter 56 Layer 2 Protocol Tunneling (L2PT) Commands ...................................................... 695
Chapter 57 Limited Multicast IP Address Commands ............................................................... 699
Chapter 58 Link Aggregation Commands .................................................................................. 708
Chapter 59 LLDP Commands .................................................................................................... 713
Chapter 60 LLDP Data Center Bridging Exchange Protocol (LLDP-DCBX) Commands .......... 736
Chapter 61 Loopback Detection Commands ............................................................................. 740
Chapter 62 Loopback Interface Commands .............................................................................. 747
Chapter 63 MAC Notification Commands .................................................................................. 750
Chapter 64 MAC-based Access Control Commands ................................................................ 755
Chapter 65 MD5 Configuration Commands ............................................................................... 771
Chapter 66 Mirror Commands.................................................................................................... 774
Chapter 67 MLD Proxy Commands ........................................................................................... 780
Chapter 68 MLD Snooping Commands ..................................................................................... 785
Chapter 69 MLD Snooping Multicast (MSM) VLAN Com mands ............................................... 802
Chapter 70 Modify Login Banner and Prompt Commands ........................................................ 813
Chapter 71 Multicast Listener Discovery (MLD) Commands ..................................................... 817
Chapter 72 Network Load Balancing (NLB) Commands ........................................................... 822
Chapter 73 Network Management Commands .......................................................................... 828
Chapter 74 Network Monitoring Commands .............................................................................. 845
Chapter 75 OAM Commands ..................................................................................................... 866
Chapter 76 Open Shortest Path First (OSPF) Command List ................................................... 873
Chapter 77 OSPFv3 Commands ............................................................................................... 895
III
Page 4
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Chapter 78
Chapter 79 Password Recovery Commands ............................................................................. 920
Chapter 80 Protocol Independent Multicast (PIM) Commands ................................................. 923
Chapter 81 PIM6-SM Commands .............................................................................................. 941
Chapter 82 Policy Route Commands ......................................................................................... 965
Chapter 83 Port Security Commands ........................................................................................ 969
Chapter 84 Power over Ethernet (PoE) Commands .................................................................. 977
Chapter 85 Power Saving Commands ....................................................................................... 982
Chapter 86 Precision Time Protocol (PTP) Commands ............................................................ 988
Chapter 87 Priority Flow Control (PFC) Commands ................................................................ 1006
Chapter 88 Protocol VLAN Commands ................................................................................... 1010
Chapter 89 Quality of Service (QoS) Commands .................................................................... 1016
Chapter 90 Q-in-Q Commands ................................................................................................ 1034
Chapter 91 Reboot Schedule Commands ............................................................................... 1047
Chapter 92 Routing Information Protocol (RIP) Commands .................................................... 1050
Chapter 93 RIPng Commands ................................................................................................. 1055
Chapter 94 RSPAN Commands............................................................................................... 1060
Packet Storm Commands ....................................................................................... 914
Chapter 95 Safeguard Engine Commands .............................................................................. 1066
Chapter 96 Secure File Transfer Protocol (SFTP) Commands ............................................... 1068
Chapter 97 sFlow Commands.................................................................................................. 1071
Chapter 98 Single IP Management Commands ...................................................................... 1082
Chapter 99 SNMPv1/v2/v3 Commands ................................................................................... 1091
Chapter 100 Spanning Tree Protocol (STP) commands ........................................................... 1110
Chapter 101 SSH Commands.................................................................................................... 1123
Chapter 102 SSL Commands .................................................................................................... 1135
Chapter 103 Stacking Commands ............................................................................................. 1142
Chapter 104 Static MAC-based VLAN Commands ................................................................... 1150
Chapter 105 Static Multicast Route Commands ........................................................................ 1153
Chapter 106 Subnet VLAN Commands ..................................................................................... 1156
Chapter 107 Super VLAN and Sub-VLAN Commands .............................................................. 1161
Chapter 108 Surveillance VLAN Commands ............................................................................. 1166
Chapter 109 Switch Port Commands ......................................................................................... 1172
Chapter 110 System Severity Commands ................................................................................. 1176
Chapter 111 Tech Support Commands ..................................................................................... 1178
Chapter 112 Time and SNTP Commands ................................................................................. 1181
Chapter 113 Traffic Segmentation Commands .......................................................................... 1188
Chapter 114 UDP Helper Commands ........................................................................................ 1190
Chapter 115 Unicast Reverse Path Forwarding (URPF) Commands ........................................ 1196
Chapter 116 Utility Commands .................................................................................................. 1201
Chapter 117 Virtual Router Redundancy Protocol (VRRP) Commands .................................... 1227
IV
Page 5
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Chapter 118
Chapter 119 VLAN Commands.................................................................................................. 1245
Chapter 120 VLAN Trunking Commands .................................................................................. 1262
Chapter 121 Web-based Access Control (WAC) Commands ................................................... 1266
Chapter 122 Weighted Random Early Detection (WRED) Commands ..................................... 1281
Appendix A Password Recovery Procedure ............................................................................. 1288
Appendix B System Log Entries ............................................................................................... 1290
Appendix C Trap Entries ........................................................................................................... 1316
Appendix D RADIUS Attributes Assignment ............................................................................. 1324
Appendix E IETF RADIUS Attributes Support .......................................................................... 1327
Voice VLAN Commands ....................................................................................... 1235
V
Page 6
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Chapter 1 Using the Command Line Interface
The DGS-3620 Layer 3 stackable Gigabit Ethernet switch series are members of the D-Link
xStack® family. Ranging from 10/100/1000Mbps edge switches to core gigabit switches, the
xStack
tolerance, flexibility, port density, robust security and maximum throughput with a user-friendly
management interface for the networking professional.
The Switch can be managed through the Switch’s serial port, Telnet, SNMP or the Web-based
management agent. The Command Line Interface (CLI) can be used to configure and manage the
Switch via the serial port or Telnet interfaces.
This manual provides a reference for all of the commands contained in the CLI. Every command
will be introduced in terms of purpose, format, description, parameters, and examples.
Configuration and management of the Switch via the Web-based management agent are
discussed in the Web UI Reference Guide. For detailed information on installing hardware please
also refer to the Harware Installation Guide.
®
switch family has been future-proof designed to provide a stacking architecture with fault
1-1 Accessing the Switch via the Ser ial Port
The Switch’s serial port’s default settings are as follows:
• 115200 baud
• no parity
• 8 data bits
• 1 stop bit
A computer running a terminal emulation program capable of emulating a VT-100 terminal and a
serial port configured as above is then connected to the Switch’s serial port via an RJ-45 to RS232 DB-9 convertor cable.
With the serial port properly connected to a management computer, the following screen should be
visible.
DGS-3620-28PC Gigabit Ethernet Switch
Command Line Interface
Firmware: Build 2.60.016
Copyright(C) 2013 D-Link Corporation. All rights reserved.
UserName:
There is no initial username or password. Just press the Enter key twice to display the CLI input
cursor − DGS-3620-28PC:admin#. This is the command line where all commands are input.
1
Page 7
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# config ipif System ipaddress 10.24.22.100/255.0.0.0
DGS-3620-28PC:admin#
1-2 Setting the Switch’s IP Address
Each Switch must be assigned its own IP Address, which is used for communication with an
SNMP network manager or other TCP/IP application (for example BOOTP, TFTP). The Switch’s
default IP address is 10.90.90.90. You can change the default Switch IP address to meet the
specification of your networking address scheme.
The Switch is also assigned a unique MAC address by the factory. This MAC address cannot be
changed, and can be found on the initial boot console screen – shown below.
Boot Procedure V1.00.016
-------------------------------------------------------------------------------
Power On Self Test ........................................ 100 %
MAC Address : 00-01-02-03-04-00
H/W Version : B1
Please Wait, Loading V2.60.016 Runtime Image .............. 100 %
UART init ................................................. 100 %
Starting runtime image
Device Discovery .......................................... 100 %
Configuration init ........................................ 100 %
Press any key to login...
The Switch’s MAC address can also be found in the Web management program on the Device
Information (Basic Settings) window on the Configuration menu.
The IP address for the S wit c h must be set before it can be managed with the Web-based manager.
The Switch IP address can be automatically set using BOOTP or DHCP protocols, in which case
the actual address assigned to the Switch must be known.
Starting at the command line prompt, enter the commands config ipif System ipaddress
xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy. Where the x’s represent the IP address to be assigned to the
IP interface named System and the y’s represent the corresponding subnet mask.
Alternatively, you can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x’s
represent the IP address to be assigned to the IP interface named System and th e z represents
the corresponding number of subnets in CIDR notation.
The IP interface named System on the Switch can be assigned an IP address and subnet mask
which can then be used to connect a management station to the Switch’s Telnet or Web-based
management agent
Command: config ipif System ipaddress 10.24.22.100/8
Success.
2
Page 8
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#?
CTRL+C ESC q Quit SPACE n Next Page ENTER Next Entry a All
DGS-3620-28PC:admin#config account
DGS-3620-28PC:admin#
In the above example, the Switch was assigned an IP address of 10.24.22.100 with a subnet mask
of 255.0.0.0. The system message Success indicates that the command was executed
successfully. The Switch can now be configured and managed via Telnet, SNMP MIB browser and
the CLI or via the Web-based management agent using the above IP address to connect to the
Switch.
There are a number of helpful features included in the CLI. Entering the ? command will display a
list of all of the top-level commands.
Command: ?
..
?
cable_diag ports
cd
cfm dm
cfm linktrace
cfm lm
cfm lock md
cfm loopback
change drive
clear
clear address_binding dhcp_snoop binding_entry ports
clear address_binding nd_snoop binding_entry ports
clear arptable
clear attack_log
clear bgp
clear bgp dampening
clear bgp flap_statistics
clear cfm dm
clear cfm lm
clear cfm pkt_cnt
clear counters
When entering a command without its required parameters, the CLI will prompt you with a Next
possible completions: message.
Command: config account
Next possible completions:
<username 15>
In this case, the command config account was entered with the parameter <username>. The CLI
will then prompt to enter the <username> with the message, Next possible completions:. Every
3
Page 9
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config account
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#the
DGS-3620-28PC:admin#
command in the CLI has this feature, and complex commands have several layers of parameter
prompting.
In addition, after typing any given command plus one space, users can see all of the next possible
sub-commands, in sequential order, by repeatedly pressing the Tab key.
To re-enter the previous command at the command prompt, press the up arrow cursor key. The
previous command will appear at the command prompt.
Command: config account
Next possible completions:
<username 15>
In the above example, the command config account was entered without the required parameter
<username>, the CLI returned the Next possible completions: <username> prompt. The up
arrow cursor control key was pressed to re-enter the previous command (config account) at the
command prompt. Now the appropriate username can be entered and the config account
command re-executed.
All commands in the CLI function in this way. In addition, the syntax of the help prompts are the
same as presented in this manual − angle brackets < > indicate a numerical value or character
string, braces { } indicate optional parameters or a choice of parameters, and brackets [ ] indicate
required parameters.
If a command is entered that is unrecognized by the CLI, the top-level commands will be displayed
under the Available commands: prompt.
Available commands:
.. ? cable_diag cd
cfm change clear config
copy create debug del
delete dir disable download
enable erase format install
login logout md move
no ping ping6 rd
reboot reconfig rename reset
save show telnet traceroute
traceroute6 upload
The top-level commands consist of commands such as show or config. Most of these commands
require one or more param eter s to narr o w the top-level command. This is equivalent to show what?
or config what? Where the what? is the next parameter.
For example, entering the show command with no additional parameters, the CLI will then display
all of the possible next parameters.
4
Page 10
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show
surveillance_vlan switch syslog system_severity
Command: show
Next possible completions:
802.1p 802.1x aaa access_profile
account accounting acct_client address_binding
arp_spoofing_prevention arpentry asymmetric_vlan
attack_log auth_client auth_diagnostics
auth_session_statistics auth_statistics authen
authen_enable authen_login authen_policy authentication
authorization autoconfig bandwidth_control bfd
bgp boot_file bpdu_protection
broadcast_ping_reply cfm command
command_history community_encryption config
cpu current_config ddm device_status
dhcp dhcp_local_relay dhcp_relay dhcp_server
dhcpv6 dhcpv6_relay dhcpv6_server dlms
dnsr dos_prevention dot1v_protocol_group
dscp duld dvmrp ecmp
egress_access_profile egress_flow_meter environment
erps error ethernet_oam external_alarm
fdb filter flow_meter gratuitous_arp
greeting_message gvrp hol_prevention host_name
igmp igmp_proxy igmp_snooping ip
ip_tunnel ipfdb ipif
ipif_ipv6_link_local_auto ipmc ipmroute
iproute ipv6 ipv6route jumbo_frame
jwac l2protocol_tunnel lacp_port led
limited_multicast_addr link_aggregation lldp
lldp_dcbx lldp_med log log_save_timing
log_software_module loopback loopdetect
mac_based_access_control mac_based_access_control_local
mac_based_vlan mac_notification max_mcast_group
mcast_filter_profile md5 mirror
mld mld_proxy mld_snooping multicast
multicast_fdb name_server nlb ospf
ospfv3 out_band_ipif packet password_recovery
per_queue pfc pim pim-ssm
pim6 poe policy_route port
port_group port_security port_security_entry
port_vlan ports power_saving private_vlan
ptp pvid qinq radius
rcp reboot rip ripng
rmon route route_map router_ports
rspan safeguard_engine scheduling
scheduling_mechanism serial_port session
sflow sftp sim snmp
sntp ssh ssl stack_device
stack_information stacking_mode storage_media_info
stp sub_vlan subnet_vlan super_vlan
5
Page 11
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
tacacs tech_support telnet terminal
DGS-3620-28PC:admin#
Syntax
Description
angle brackets < >
Encloses a variable or value. Users must specify the variable or value.
square brackets [ ]
Encloses a required value or list of required arguments. Only on e
vertical bar |
Separates mutually exclusive items in a list. For example, in the syntax
braces { }
Encloses an optional value or a list of optional arguments. One or
tftp time time_range traffic
traffic_segmentation trap trusted_host
udp_helper utilization vlan vlan_precedence
vlan_translation vlan_translation_profile vlan_trunk
voice_vlan vrrp wac wred
In the above example, all of the possible next parameters for the show command are displayed. At
the next command prompt, the up arrow was used to re-enter the show command, followed by the
account parameter. The CLI then displays the user accounts configured on the Switch.
1-3 Command Syntax Symbols
The following symbols are used to describe how command entries are made and values and
arguments are specified in this manual. The online help contained in the CLI and available through
the console interface uses the same syntax.
Note: All commands are case-sensitive. Be sure to disable Caps Lock or any other unwanted
function that changes text case.
For example, in the syntax
create ipif <ipif_name 12> {<network_address>} <vlan_name 32>
{secondary | state [enable | disable] | proxy_arp [enable | disable]
{local [enable | disable]}}
users must supply an IP interface name for <ipif_name 12> and a
VLAN name for <vlan_name 32> when entering the command. DO
NOT TYPE THE ANGLE BRACKETS.
value or argument must be specified. For example, in the syntax
create account [admin | operator | power_user | user] <username
15> {encrypt [plain_text | sha_1] <password>}
users must specify either the admin-, operator-, power_user-level or
user-level account when entering the command. DO NOT TYPE THE
SQUARE BRACKETS.
reset {[config | system]} {force_agree}
users may choose config or system in the command. DO NOT TYPE
THE VERTICAL BAR.
more values or arguments can be specified. For example, in the syntax
reset {[config | system]} {force_agree}
users may choose config or system in the command. DO NOT TYPE
THE BRACES.
6
Page 12
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
parentheses ( )
Indicates at least one or more of the values or arguments in the
ipif <ipif_name 12>
12 means the maximum length of the IP interface name.
Keys
Description
Delete
Delete character under cursor and shift remainder of line to left.
Backspace
Delete character to left of cursor and shift remainder of line to left.
CTRL+R
Toggle on and off. When toggled on, inserts text and shifts previous
Up Arrow
Repeats the previously entered command. Each time the up arrow is
Down Arrow
The down arrow will display the next command in the command history
Left Arrow
Move cursor to left.
Right Arrow
Move cursor to right
Tab
Help user to select appropriate token.
Keys
Description
Space
Displays the next page.
CTRL+C
Stops the display of remaining pages when multiple pages are to be
ESC
Stops the display of remaining pages when multiple pages are to be
n
Displays the next page.
p
Displays the previous page.
preceding syntax enclosed by braces must be specified. For example,
in the syntax
config dhcp_relay {hops <int 1-16> | time <sec 0-65535>}(1)
users have the option to specify hops or time or both of them. The "(1)"
following the set of braces indicates at least one argum ent or value
within the braces must be specified. DO NOT TYPE THE
PARENTHESES.
metric <value 1-31>
1-31 means the legal range of the metric value.
1-4 Line Editing Keys
text to right.
pressed, the command previous to that displayed appears. This way it is
possible to review the command history for the current session. Use the
down arrow to progress sequentially forward through the command
history list.
entered in the current session. This displays each command sequentially
as it was entered. Use the up arrow to review previous commands.
The screen display pauses when the show command output reaches the end of the page.
1-5 Multiple Page Display Control Keys
displayed.
displayed.
7
Page 13
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
q
Stops the display of remaining pages when multiple pages are to be
r
Refreshes the pages currently displayed.
a
Displays the remaining pages without pausing between pages.
Enter
Displays the next line or table entry.
displayed.
8
Page 14
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
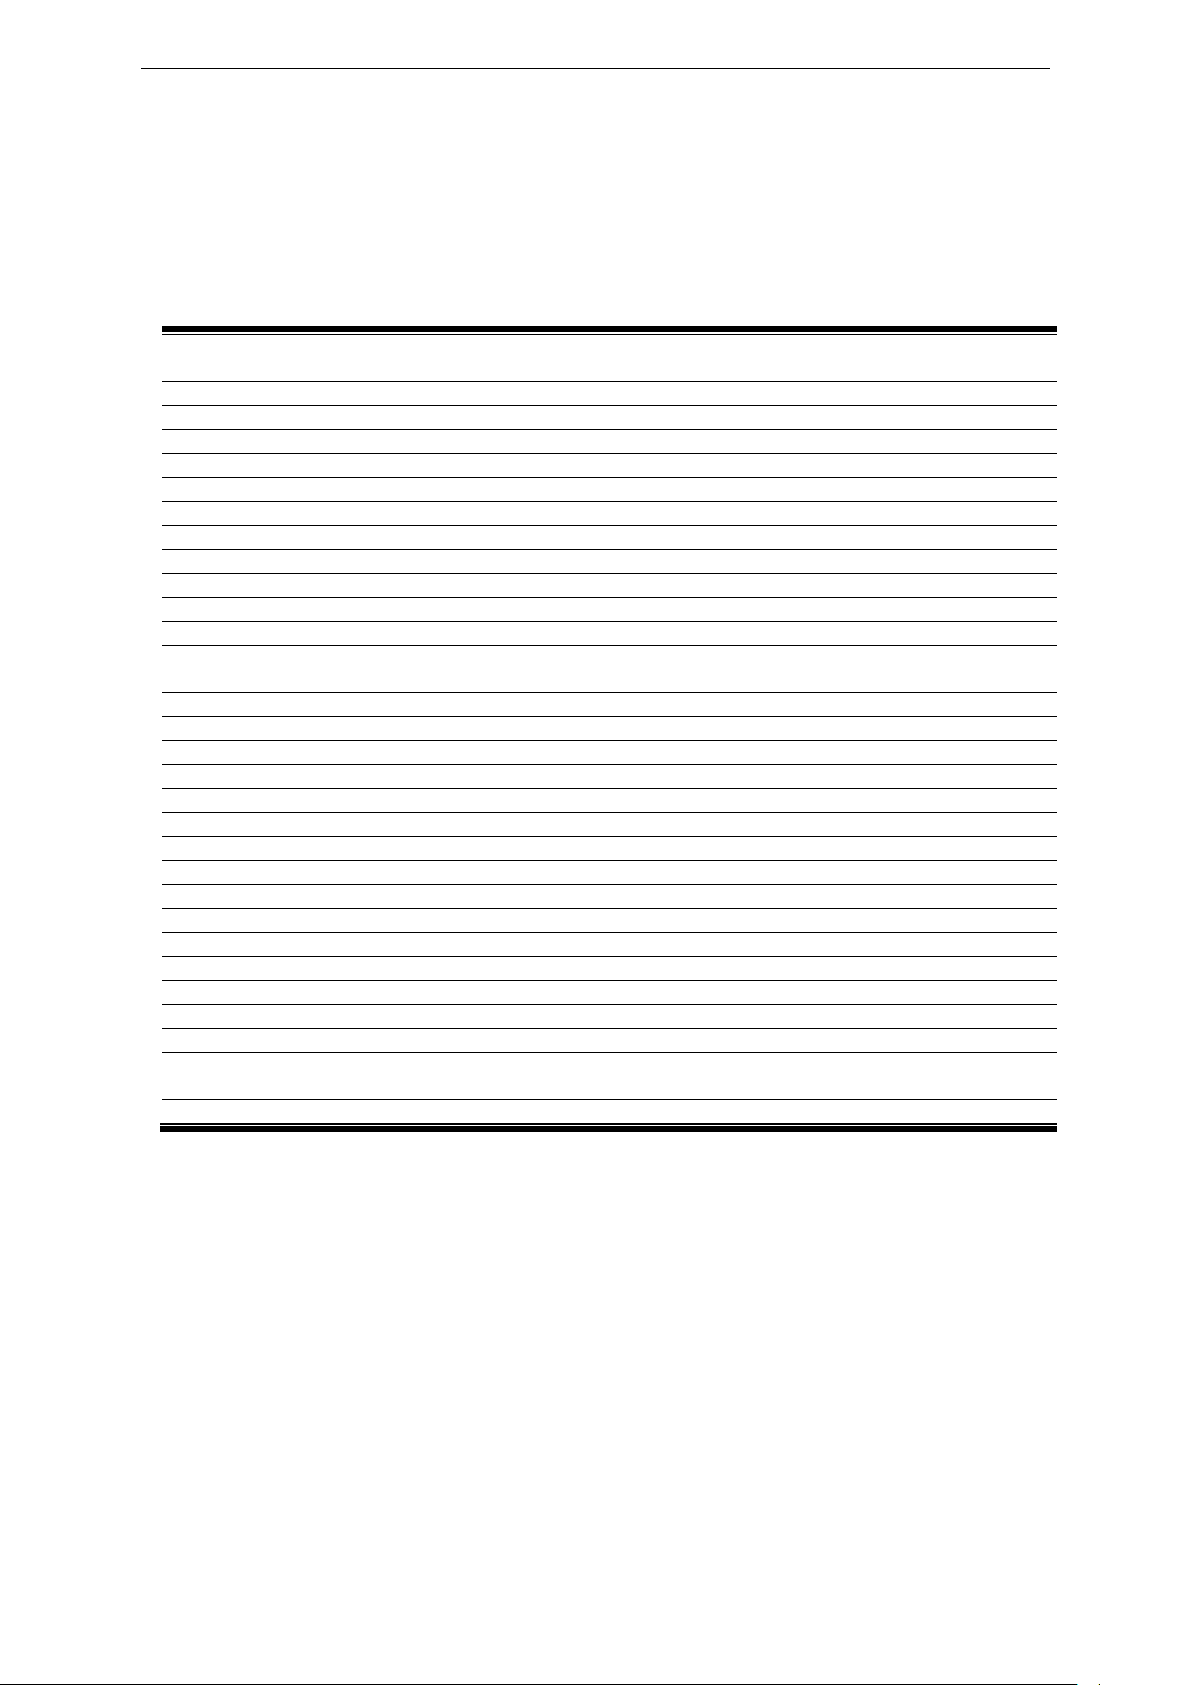
create account [admin | operator | power_user | user] <username 15> {encrypt [plain_text |
sha_1] <password>}
enable password encryption
disable password encryption
config account <username 15> {encrypt [plain_text | sha_1] <password>}
show account
delete account <username 15>
show session
show switch
show environment
config temperature [trap | log] state [enable | disable]
config temperature threshold {high <temperature -500-500> | low <temperature -500-500>}(1)
show serial_port
config serial_port { bau d_r at e [960 0 | 19200 | 38400 | 1152 00] | auto_l ogo ut [never | 2_minutes |
5_minutes | 10_minutes | 15_m inutes ]}( 1)
enable clipaging
disable clipaging
enable telnet {<tcp_port_number 1-65535>}
disable telnet
enable web {<tcp_port_number 1-65535>}
disable web
save {[config <pathname> | log | all]}
reboot {force_agree}
reset {[config | system]} {force_agree}
login
logout
clear
config terminal width [default | <value 80-200>]
show terminal width
show device_status
config out_band_ipif {ipaddress <network_address> | state [enab le | disable] | gate wa y
<ipaddr>}
show out_band_ipif
Chapter 2 Basic Management Commands
2-1 create account
Description
This command creates user accounts. The username is between 1 and 15 characters, the
password is between 0 and 15 characters. The number of accounts (including admin, operator,
and user) is up to eight.
Format
create account [admin | operator | power_user | user] <username 15> {encrypt [plain_text |
sha_1] <password>}
9
Page 15
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
admin - Specifies the name of the admin account.
operator - Specifies the name of the operator account.
power_user - Specifies a power user level account. The power user level is lower than the
operator level and higher than the user level.
user - Specifies the name of the user account.
<username 15> - Enter a username of up to 15 characters.
encrypt - Specifies the enc ryption used.
password, the length is fixed to 35 bytes long. The password is case-sensitive.
DGS-3620-28PC:admin#create account admin dlink
DGS-3620-28PC:admin#
DGS-3620-28PC:admin##create account operator Sales
DGS-3620-28PC:admin#
DGS-3620-28PC:admin##create account user System
DGS-3620-28PC:admin#
Parameters
plain_text - Specifies the password in plain text form.
sha_1 - Specifies the password in SHA-1 encrypted form.
<password> - The password for the user account. The length of a password in plain-text form
and encrypted form are different. For a plain-text form password, the password must be a
minimum of 0 characters and a maximum of 15 characters. For an encrypted form
Restrictions
Only Administrator-level users can issue this command.
Example
To create the Administrator-level user “dlink”:
Command: create account admin dlink
Enter a case-sensitive new password:****
Enter the new password again for confirmation:****
Success.
To create the Operator-level user “Sales”:
Command: create account operator Sales
Enter a case-sensitive new password:****
Enter the new password again for confirmation:****
Success.
To create the User-lev el us er “System”:
Command: create account user System
Enter a case-sensitive new password:****
Enter the new password again for confirmation:****
Success.
10
Page 16
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable password encryption
DGS-3620-28PC:admin#
2-2 enable password encryption
Description
The user account configuration information will be stored in the configuration file, and can be
applied to the system later. If the password encryption is enabled, the password will be in
encrypted form when it is stored in the configuration file. When password encryption is disabled,
the password will be in plain text form when it is stored in the configuration file. However, if the
created user account directly uses the encrypted password, the password will still be in the
encrypted form.
Format
enable password encryption
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To enable password encryption:
Command: enable password encryption
Success.
2-3 disable password encryption
Description
The user account configuration information will be stored in the configuration file, and can be
applied to the system later. If the password encryption is enabled, the password will be in
encrypted form when it is stored in the configuration file. When password encryption is disabled,
the password will be in plain text form when it is stored in the configuration file. However, if the
created user account directly uses the encrypted password, the password will still be in the
encrypted form.
Format
disable password encryption
Parameters
None.
11
Page 17
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#disable password encryption
DGS-3620-28PC:admin#
<username 15> - Enter the name of the account. The account must already be defined.
encrypt - (Optional) Spec if ies the encryption type, plain_text or sha_1.
password, the length is fixed to 35 bytes long. The password is case-sensitive.
<password> - Enter the password.
DGS-3620-28PC:admin#config account dlink
Enter the new password again for confirmation:****
Restrictions
Only Administrator-level users can issue this command.
Example
To disable password encryption:
Command: disable password encryption
Success.
2-4 config account
Description
When the password information is not specified in the command, the system will prompt the user
to input the password interactively. For this case, the user can only input the plain text password.
If the password is present in the command, the user can select to input the password in the plain
text form or in the encrypted form. The encryption algorithm is based on SHA-1.
Format
config account <username 15> {encrypt [plain_text | sha_1] <password>}
Parameters
plain_text - Specifies the password in plain text form. For the plain text form, passwords must
have a minimum of 0 and a maximum of 15 characters. The password is case-sensitive
sha_1 - Specifies the password in the SHA-1 encrypted form. For the encrypted form
Restrictions
Only Administrator-level users can issue this command.
Example
To configure the user password of the “dlink” account:
Command: config account dlink
Enter a old password:****
Enter a case-sensitive new password:****
12
Page 18
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Success.
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#config account administrator encrypt sha_1
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show account
DGS-3620-28PC:admin#
To configure the user password of the “administrator” account:
*@&NWoZK3kTsExUV00Ywo1G5jlUKKv+toYg
Command: config account administrator encrypt sha_1
*@&NWoZK3kTsExUV00Ywo1G5jlUKKv+toYg
Success.
2-5 show account
Description
This command is used to display user accounts that have been created.
Format
show account
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To display accounts that have been created:
Command: show account
Current Accounts:
Username Access Level
--------------- -----------System User
Sales Operator
dlink Admin
2-6 delete account
Description
This command is used to delete an existing account.
13
Page 19
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<username 15> - Enter the name of the user who will be deleted.
DGS-3620-28PC:admin#delete account System
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show session
8 23:37:42.270 Serial Port admin Anonymous
Format
delete account <username 15>
Parameters
Restrictions
Only Administrator-level users can issue this command. One active admin user must exist.
Example
To delete the user account “System”:
Command: delete account System
Success.
2-7 show session
Description
This command is used to display a list of current users which are logged in to CLI sessions.
Format
show session
Parameters
None.
Restrictions
Only Administrators and Operators can issue this command.
Example
To display accounts a list of currently logged-in users:
Command: show session
ID Live Time From Level User
-- ------------ ------------ ----- --------------------
14
Page 20
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
DGS-3620-28PC:admin#show switch
DVMRP : Disabled
Total Entries: 1
2-8 show switch
Description
This command is used to display the switch inform ation.
Format
show switch
Parameters
None.
Restrictions
None.
Example
To display the switch information:
Command: show switch
Device Type : DGS-3620-28PC Gigabit Ethernet Switch
MAC Address : 00-01-02-03-04-00
IP Address : 10.90.90.90 (Manual)
VLAN Name : default
Subnet Mask : 255.0.0.0
Default Gateway : 0.0.0.0
Boot PROM Version : Build 1.00.016
Firmware Version : Build 2.60.016
Hardware Version : B1
Firmware Type : EI
Serial Number : D1234567890
System Name :
System Location :
System Uptime : 0 days, 0 hours, 7 minutes, 13 seconds
System Contact :
Spanning Tree : Disabled
GVRP : Disabled
IGMP Snooping : Disabled
MLD Snooping : Disabled
RIP : Disabled
RIPng : Disabled
15
Page 21
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
PIM : Disabled
DGS-3620-28PC:admin#
PIM6 : Disabled
PIM6 : Disabled
OSPFv3 : Disabled
BGP : Disabled
VLAN Trunk : Disabled
Telnet : Enabled (TCP 23)
Web : Enabled (TCP 80)
SNMP : Disabled
SSL Status : Disabled
SSH Status : Disabled
802.1X : Disabled
Jumbo Frame : Off
CLI Paging : Enabled
MAC Notification : Disabled
Port Mirror : Disabled
SNTP : Disabled
DHCP Relay : Disabled
DNSR Status : Disabled
VRRP : Disabled
HOL Prevention State : Enabled
Syslog Global State : Disabled
Single IP Management : Disabled
Password Encryption Status : Disabled
DNS Resolver : Disabled
2-9 show environment
Description
This command is used to display the device’s internal and external power, internal temperature,
and fan status.
Format
show environment
Parameters
None.
Restrictions
None.
Example
To display the switch hardware and fan status:
16
Page 22
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# show environment
DGS-3620-28PC:admin#
trap - Specifies to configure the warning temperature trap.
log - Specifies to configure t he war ning temperature log.
state - Enable or disable either the trap or log state for a warning temperature event. The default
disable - Disable either the trap or log state for a warning temperature event.
DGS-3620-28PC:admin#config temperature trap state enable
DGS-3620-28PC:admin#
Command: show environment
High Warning Temperature Threshold(Celsius) : 79
Low Warning Temperature Threshold(Celsius) : 11
Unit 1
Internal Power : Active
External Power : Fail
Right Fan 1 : Speed Low (3000 RPM)
Right Fan 2 : Speed Low (3000 RPM)
Right Fan 3 : Speed Low (3000 RPM)
Right Fan 4 : Speed Low (3000 RPM)
Current Temperature(Celsius) : 28
Fan High Temperature Threshold(Celsius) : 40
Fan Low Temperature Threshold(Celsius) : 35
2-10 config temperature
Description
This command is used to configure the warning trap or log state of the system internal temperature.
Format
config temperature [trap | log] state [enable | disable]
Parameters
is enable.
enable - Enable either the trap or log state for a warning temperature event.
Restrictions
Only Administrators and Operators can issue this command.
Example
To enable the warning temperature trap state:
Command: config temperature trap state enable
Success.
17
Page 23
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config temperature log state enable
DGS-3620-28PC:admin#
high - Specifies the high threshold value. The high threshold must bigger than the low threshold.
and 500.
low - Specifies the lo w thres hold va lue .
and 500.
DGS-3620-28PC:admin#config temperature threshold high 80
DGS-3620-28PC:admin#
To enable the warning temperature log state:
Command: config temperature log state enable
Success.
2-11 config temperature threshold
Description
This command is used to configure the warning temperature high threshold or low threshold. When
temperature is above the high threshold or below the low threshold, SW will send alarm traps or
keep the logs.
Format
config temperature threshold {high <temperature -500-500 > | low <temp erat ure -500-500>}(1)
Parameters
<temperature -500-500> - Enter the high thr esho ld va l ue. This value must be between -500
<temperature -500-500> - Enter the low threshold value. This value must be between -500
Restrictions
Only Administrators and Operators can issue this command.
Example
To configure a warming temperature threshold high of 80:
Command: config temperature threshold high 80
Success.
2-12 show serial_ port
Description
This command is used to display the current console port setting.
18
Page 24
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show serial_port
DGS-3620-28PC:admin#
baud_rate - Specifies the baud rate value. The default baud rate is 115200.
115200 - Specifies a baud rate of 115200.
auto_logout - Specifies the timeout value. The default timeout is 10_minutes.
15_minutes - Specifies when the idle value is over 15 minutes, the device will auto logout.
Format
show serial_port
Parameters
None.
Restrictions
None.
Example
To display the console port setting:
Command: show serial_port
Baud Rate : 115200
Data Bits : 8
Parity Bits : None
Stop Bits : 1
Auto-Logout : 10 mins
2-13 config serial_port
Description
This command is used to configure the serial bit rate that will be used to communicate with the
management host and the auto logout time for idle connections.
Format
config serial_port {baud_rate [9600 | 19200 | 38400 | 115200] | auto_logout [never |
2_minutes | 5_minutes | 10_minutes | 15_minutes]}(1)
Parameters
9600 - Specifies a baud rate of 9600.
19200 - Specifies a baud rate of 19200.
38400 - Specifies a baud rate of 38400.
never - Specifies to never timeout.
2_minutes - Specifies when the idle value is over 2 m inutes , the de vice w ill auto l ogou t .
5_minutes - Specifies when the idle value over 5 minutes, the device will auto logout.
10_minutes - Specifies when the idle value is over 10 minutes, the device will auto logout.
19
Page 25
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# config serial_port baud_rate 9600
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#enable clipaging
DGS-3620-28PC:admin#
Restrictions
Only Administrators and Operators can issue this command.
Example
To configure the baud rate:
Command: config serial_port baud_rate 9600
Success.
2-14 enable clipaging
Description
This command is used to enable pausing of the screen display when show command output
reaches the end of the page. The default setting is enabled.
Format
enable clipaging
Parameters
None.
Restrictions
Only Administrators and Operators can issue this command.
Example
To enable pausing of the screen display when show command output reaches the end of the page:
Command: enable clipaging
Success.
2-15 disable clipaging
Description
This command is used to disable pausing of the screen display when show command output
reaches the end of the page. The default setting is enabled.
20
Page 26
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#disable clipaging
DGS-3620-28PC:admin#
<tcp_port_number 1-65535> - (Optional) Specifies the TCP port number. TCP ports are
numbered between 1 and 65535. The “well-known” TCP port for the Telnet protocol is 23.
DGS-3620-28PC:admin#enable telnet 23
DGS-3620-28PC:admin#
Format
disable clipaging
Parameters
None.
Restrictions
Only Administrators and Operators can issue this command.
Example
To disable pausing of the screen display when show comm and output r eac hes th e end of the page:
Command: disable clipaging
Success.
2-16 enable telnet
Description
This command is used to enable Telnet and configure a port num ber . The default setting is
enabled and the port number is 23.
Format
enable telnet {<tcp_port_number 1-65535>}
Parameters
Restrictions
Only Administrators and Operators can issue this command.
Example
To enable Telnet and configure a port number:
Command: enable telnet 23
Success.
21
Page 27
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#disable telnet
DGS-3620-28PC:admin#
<tcp_port_number 1-65535> - (Optional) Specif ies the TCP port number. TCP ports are
numbered between 1 and 65535. The “well-know” TCP port for the Web protocol is 80.
2-17 disable telnet
Description
This command is used to disable Telnet.
Format
disable telnet
Parameters
None.
Restrictions
Only Administrators and Operators can issue this command.
Example
To disable Telnet:
Command: disable telnet
Success.
2-18 enable web
Description
This command is used to enable Web UI and configure the port number. The default setting is
enabled and the port number is 80.
Format
enable web {<tcp_port_number 1-65535>}
Parameters
Restrictions
Only Administrators and Operators can issue this command.
22
Page 28
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable web 80
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#disable web
DGS-3620-28PC:admin#
Example
To enable HTTP and configure port number:
Command: enable web 80
Note: SSL will be disabled if web is enabled.
Success.
2-19 disable web
Description
This command is used to disable Web UI.
Format
disable web
Parameters
None.
Restrictions
Only Administrators and Operators can issue this command.
Example
To disable HTTP:
Command: disable web
Success.
2-20 save
Description
This command is used to save the current configuration or log in non-volatile RAM.
Format
save {[config <pathname> | log | all]}
23
Page 29
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
config - (Optional) Specifies to save configuration.
<pathname> - Enter the path name of the indicated configuration
log - (Optional) Specifies to save log.
all - (Optional) Specifies to save changes to currently active configuration and save logs.
Note: If no keyword is specified, all changes will be saved to bootup configuration file.
DGS-3620-28PC:admin#save
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#save config 1
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#save log
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#save all
DGS-3620-28PC:admin#
Parameters
Restrictions
Only Administrators and Operators can issue this command.
Example
To save the current configuration to the bootup configuration file:
Command: save
Saving all configurations to NV-RAM.......... Done.
To save the current configuration to destination file, named 1:
Command: save config 1
Saving all configurations to NV-RAM.......... Done.
To save a log to NV-RAM:
Command: save log
Saving all system logs to NV-RAM............. Done.
To save all the configurations and logs to NV-RAM:
Command: save all
Saving configuration and logs to NV-RAM...... Done.
24
Page 30
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
force_agree – (Optional) Specify to immediately execute the reboot command without further
confirmation.
DGS-3620-28PC:admin#reboot
Please wait, the switch is rebooting…
config - (Optional) Specifies this keyword and all parameters are reset to default settings.
However, the device will neither save nor reboot.
system - (Optional) Spec if i es this keyword and all parameters are reset to default settings. Then
the switch will do factory reset, save, and reboot.
force_agree - (Optional) Specifies and the reset command will be executed immediately without
further confirmation.
Note: If no keyword is specified, all parameters will be reset to default settings except IP
2-21 reboot
Description
This command is used to restart the switch.
Format
reboot {force_agree}
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To restart the switch:
Command: reboot
Are you sure you want to proceed with the system reboot?(y/n)
2-22 reset
Description
This command is used to reset all switch parameters to the factory defaults.
Format
reset {[config | system]} {force_agree}
Parameters
address, user account, and history log, but the device will neither save nor reboot.
25
Page 31
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#reset
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#reset config
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#reset system
Please wait, the switch is rebooting…
Restrictions
Only Administrator-level users can issue this command.
Example
To reset all the switch parameters except the IP address:
Command: reset
Are you sure to proceed with system reset except IP address?(y/n)
Success.
To reset the system configuration settings:
Command: reset config
Are you sure to proceed with system reset?(y/n)
Success.
To reset all system parameters, save, and restart the switch:
Command: reset system
Are you sure to proceed with system reset, save and reboot?(y/n)
Loading factory default configuration… Done.
Saving all configuration to NV-RAM… Done.
2-23 login
Description
This command is used to log in to the switch.
Format
login
Parameters
None.
Restrictions
None.
26
Page 32
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#login
UserName:
DGS-3620-28PC:admin#logout
Example
To login to the switch:
Command: login
2-24 logout
Description
This command is used to log out of the switch.
Format
logout
Parameters
None.
Restrictions
None.
Example
To logout of the switch:
Command: logout
***********
* Logout *
***********
UserName:
DGS-3620-28PC Gigabit Ethernet Switch
Command Line Interface
Firmware: Build 2.60.016
Copyright(C) 2013 D-Link Corporation. All rights reserved.
27
Page 33
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#clear
Command: clear
default - Specifies the default terminal width value.
<value 80-200> - Enter a terminal width value between 80 and 200 characters. The default value
is 80.
DGS-3620-28PC:admin#config terminal width 90
Command: config terminal width 90
2-25 clear
Description
This command is used to clear the terminal screen.
Format
clear
Parameters
None.
Restrictions
None.
Example
To clear the terminal screan:
2-26 config terminal width
Description
This command is used to configure the terminal width.
Format
config terminal width [defa ult | < value 8 0-200>]
Parameters
Restrictions
None.
Example
To configure the terminal width:
28
Page 34
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show terminal width
DGS-3620-28PC:admin#
Success.
2-27 show terminal width
Description
This command is used to display the configuration of the current terminal width.
Format
show terminal width
Parameters
None.
Restrictions
None.
Example
To display the configuration of the current terminal width:
Command: show terminal width
Global terminal width : 80
Current terminal width : 80
2-28 show device_status
Description
This command displays current status of power(s) and fan(s) on the system.
Within fan(s) status display, for example, there are three fans on the left of the switch, if three fans
is working normally, there will display “OK” in the Left Fan field. If some fans work failed, such as
fan 1,3 , there will only display the failed fans in the Left Fan field, such as “1,3 Fail”.
In the same way, the Right Fan, Back Fan is same to Left Fan. Because there is only one CPU
Fan, if it is working failed, display “Fail”, otherwise display “OK”.
Format
show device_status
29
Page 35
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# show device_status
DGS-3620-28PC:admin#
ipaddress - Specifies the IP address of the interface. The parameter must include the mask.
mask.
state – Specify the interface status.
disable - Specifies to disable the interface.
gateway - Specifies the gateway IP address of the out-of-band management network.
Parameters
None.
Restrictions
None.
Example
To show device status, the number 1, 2, 3 etc represent the fan number:
Command: show device_status
Unit 1:
Internal Power: Active
External Power: Fail
Left Fan : 1, 3 Fail
Right Fan : 2 Fail
Back Fan : OK
CPU Fan : Fail
Unit 2:
Internal Power: Active
External Power: Fail
Left Fan : 1 Fail
Right Fan : OK
Back Fan : 2, 4 Fail
CPU Fan : OK
2-29 config out_band_ip if
Description
This command is used to configure the out of band management port settings.
Format
config out_band_ipif {ipaddress <network_address> | state [enable | disable] | gate way
<ipaddr>} (1)
Parameters
<network_address> - Enter the IP address of the interface. The parameter must include the
enable - Specifies to enable the interface.
30
Page 36
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<ipaddr> - Enter the gateway IP address.
DGS-3620-28PC:admin#config out_band_ipif state disable
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show out_band_ipif
DGS-3620-28PC:admin#
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To disable the out-of-band management state:
Command: config out_band_ipif state disable
Success.
2-30 show out_band_ipi f
Description
This command is used to display the current configurations of special out-of-band management
interfaces.
Format
show out_band_ipif
Parameters
None.
Restrictions
None.
Example
To display the configuration of out-of-band management interfaces:
Command: show out_band_ipif
Status : Enable
IP Address : 192.168.0.1
Subnet Mask : 255.255.255.0
Gateway : 0.0.0.0
Link Status : LinkDown
31
Page 37
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
enable 802.1x
disable 802.1x
create 802.1x user <username 15>
delete 802.1x user <username 15>
show 802.1x user
config 802.1x auth_protocol [local | radius_eap]
show 802.1x {[auth_state | auth_configuration] ports {<portlist>}}
config 802.1x capability ports [<portlist> | all] [authenticator | none]
config 802.1x fwd_pdu ports [<portlist> | all] [enable | disable]
config 802.1x fwd_pdu system [enable | disable]
config 802.1x auth_parameter ports [<portlist> | all] [default | {direct ion [bot h | in] | port_contr o l
| disable]}(1)]
config 802.1x authorization attributes radius [enable | disable]
config 802.1x init [port_based ports [<portlist> | all] | mac_based ports [<portlist> | all]
{mac_address <macaddr>}]
config 802.1x max_users [<value 1-448> | no_limit]
config 802.1x reauth [port_based ports [<portlist> | all] |mac_based ports [<portlist> | all]
{mac_address <macaddr>}]
create 802.1x guest_vlan <vlan_name 32>
delete 802.1x guest_vlan <vlan_name 32>
config 802.1x guest_vlan ports [<portlist> | all] state [enable | disable]
show 802.1x guest_vlan
config 802.1x trap state [enable | disable]
config radius add <server_index 1-3> [<server_ip> |<ipv6addr>] [key <password 32> |
<udp_port_number 1-65535> | timeout <sec 1-255> | retransmit <int 1-20>}]
config radius delete <server_index 1-3>
config radius <server_index 1-3> {ipaddress [<server_ip> |<ipv6addr>] | [key <password 32> |
[<int 1-20> | default]}
show radius
show auth_statistics {ports <portlist>}
show auth_diagnostics {ports <portlist>}
show auth_session_statistics {ports <portlist>}
show auth_client
show acct_client
Chapter 3 802.1X Commands
[force_unauth | auto | force_auth] | quiet_period <sec 0-655 35 > | tx_per iod <sec 1-65535> |
supp_timeout <sec 1-65535> | server_timeout <sec 1-65535> | max_req <value 1-10> |
reauth_period <sec 1-65535> | max_users [<value 1-448> | no_limit] | enable_r e a uth [ena ble
encryption_key <password 56>] [default | {auth_port <udp_port_number 1-65535> | acct_port
encryption_key <password 56>] | auth_port [<udp_port_number 1-65535> | default] |
acct_port [<udp_port_number 1-65535> | default] | timeout [<sec 1-255> | default] | retrans mit
3-1 enable 802.1x
Description
This command is used to enable the 802.1X function.
Format
enable 802.1x
32
Page 38
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable 802.1x
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#disable 802.1x
DGS-3620-28PC:admin#
Parameters
None.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To enable the 802.1X function:
Command: enable 802.1x
Success.
3-2 disable 802.1x
Description
This command is used to disable the 802.1X function.
Format
disable 802.1x
Parameters
None.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To disable the 802.1Xfunction:
Command: disable 802.1x
Success.
33
Page 39
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<username 15> - Enter to add a user name.
DGS-3620-28PC:admin#create 802.1x user ctsnow
DGS-3620-28PC:admin#
<username 15> - Enter to delete a user name.
3-3 create 802.1x user
Description
This command is used to create an 802.1X user.
Format
create 802.1x user <username 15>
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To create a user named “ctsnow”:
Command: create 802.1x user ctsnow
Enter a case-sensitive new password:
Enter the new password again for confirmation:
Success.
3-4 delete 802.1x user
Description
This command is used to delete a specified user.
Format
delete 802.1x user <username 15>
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
34
Page 40
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#delete 802.1x user Tiberius
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show 802.1x user
DGS-3620-28PC:admin#
Example
To delete the user named “Tiberius”:
Command: delete 802.1x user Tiberius
Success.
3-5 show 802.1x user
Description
This command is used to display 802.1X local user account information.
Format
show 802.1x user
Parameters
None.
Restrictions
None.
Example
To display 802.1X user information:
Command: show 802.1x user
Current Accounts:
Username Password
--------------- -----------ctsnow gallinari
Total Entries : 1
3-6 config 802.1x auth_protocol
Description
This command is used to configure the 802.1X authentication protocol.
35
Page 41
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
local - Specifiy the authentication protocol as local.
radius_eap - Specifies the authentication protoco l as RADIU S EA P.
DGS-3620-28PC:admin#config 802.1x auth_protocol radius_eap
DGS-3620-28PC:admin#
auth_state - (Optional) Specifies to display the 802.1X authentication state of some or all ports.
auth_configuration - (Optional) Specifies to display 802.1X configuration of some or all ports.
ports - (Optional) Specifies a range of ports to be displayed.
<portlist> - Enter a range of ports to be displayed.
DGS-3620-28PC:admin#show 802.1x
802.1X : Disabled
Format
config 802.1x auth_protocol [l o cal | radius_eap]
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the 802.1X RADIUS EAP:
Command: config 802.1x auth_protocol radius_eap
Success.
3-7 show 802.1x
Description
This command is used to display the 802.1X state or configurations.
Format
show 802.1x {[auth_state | auth_configuration] ports {<portlist>}}
Parameters
Restrictions
None.
Example
To display 802.1X information:
Command: show 802.1x
36
Page 42
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Authentication Protocol : RADIUS_EAP
DGS-3620-28PC:admin#
DGS-3620-28PC:admin# show 802.1x auth_state ports 1-4
DGS-3620-28PC:admin#
DGS-3620-28PC:admin# show 802.1x auth_configuration ports 1:1
DGS-3620-28PC:admin#
Forward EAPOL PDU : Disabled
Max User : 448
RADIUS Authorization : Enabled
To display the 802.1x state for ports 1 to 5:
Command: show 802.1x auth_state ports 1-4
Status: A – Authorized; U – Unauthorized; (P): Port-Based 802.1X Pri: Priority
Port MAC Address Auth PAE State Backend Status VID Pri
VID State
----- -------------------- ------- -------------- ---------- ------ ----- ----1 00-00-00-00-00-01 10 Authenticated Idle A 4004 3
1 00-00-00-00-00-02 10 Authenticated Idle A 1234 1 00-00-00-00-00-04 30 Authenticating Response U - 2 - (P) - Authenticating Request U - 3 - (P) - Connecting Idle U - 4 - (P) - Held Fail U - -
Total Authenticating Hosts: 3
Total Authenticated Hosts : 2
To display the 802.1x configuration for port 1:
Command: show 802.1x auth_configuration ports 1:1
Port number : 1:1
Capability : None
AdminCrlDir : Both
OpenCrlDir : Both
Port Control : Auto
QuietPeriod : 60 Seconds
TxPeriod : 30 Seconds
SuppTimeout : 30 Seconds
ServerTimeout : 30 Seconds
MaxReq : 2 Times
ReAuthPeriod : 3600 Seconds
ReAuthenticate : Disabled
Forward EAPOL PDU On Port : Enabled
Max User On Port : 10
37
Page 43
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<portlist> - Enter a range of ports to be configured.
all - Specifies to configure all ports.
authenticator - The port that wishes to enforce authentication before allowing access to services
that are accessible via that port adopts the authenticator role.
none – Disable authentication on specified port.
DGS-3620-28PC:admin#config 802.1x capability ports 1-10 authenticator
DGS-3620-28PC:admin#
<portlist> - Enter a range of ports to be configured.
all - Specifies all ports.
enable - Enable the 802.1X PDU forwarding state.
disable - Disable the 802.1X PDU forwarding state.
3-8 config 802.1x capability port s
Description
This command is used to configure port capability.
Format
config 802.1x capability ports [< p o rtlist> | all] [authenticator | none]
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure port capability for ports 1 to 10:
Command: config 802.1x capability ports 1-10 authenticator
Success.
3-9 config 802.1x fwd_pdu ports
Description
This command is used to configure the 802.1X PDU forwarding state on specific ports of the
switch.
Format
config 802.1x fwd_pdu ports [<portlist> | all] [enable | disable]
Parameters
38
Page 44
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config 802.1x fwd_pdu ports 1-2 enable
DGS-3620-28PC:admin#
enable - Enable the 802.1X PDU forwarding state.
disable - Disable the 802.1X PDU forwarding state.
DGS-3620-28PC:admin#config 802.1x fwd_pdu system enable
DGS-3620-28PC:admin#
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the 802.1X PDU forwarding state on ports 1 to 2:
Command: config 802.1x fwd_pdu ports 1-2 enable
Success.
3-10 config 802.1x fwd_ pdu s y stem
Description
This command is used to configure the 802.1X PDU forwarding state.
Format
config 802.1x fwd_pdu system [enable | disable]
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the 802.1X PDU forwarding state:
Command: config 802.1x fwd_pdu system enable
Success.
3-11 config 802.1x auth_parameter ports
Description
This command is used to configure the parameters that control the operation of the authenticator
associated with a port.
39
Page 45
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<portlist> - Enter a range of ports to be configured.
all - Specifies to configure all ports.
default - Set all parameters to the default value.
direction - (Optional) Set the direction of access control.
in - For ingress access control.
port_control - (Optional) Force a specific port to be unconditionally authorized or unauthorized
client to authenticate.
quiet_period - (Optional) The initialization value of the quietWhile timer. The default value is 60 s
<sec 0-65535> - The quiet period value must be between 0 an 65535 seconds.
tx_period - (Optional) The initialization value of the txWhen timer. The default value is 30 s and
<sec 1-65535> - The transmit period value must be between 1 an 65535 seconds.
supp_timeout - (Optional) The initialization value of the aWhile timer when timing out the
<sec 1-65535> - The timeout value must be between 1 an 65535 seconds.
server_timeout - (Optional) The initialization value of the aWhile timer when timing out the
<sec 1-65535> - The server timeout value must be between 1 an 65535 seconds.
max_req - (Optional) The maximum number of times that the authenitcation PAE state machine
<value 1-10> - The maximum require number must be between 1 and 10.
reauth_period - (Optional) It's a non-zero number of seconds, which is used to be the re-
<sec 1-65535> - The reauthentication period value must be between 1 an 65535 seconds.
max_users - (Optional) Set the maximum number of users between 1 and 448.
no_limit - Set an unlimited number of users.
enable_reauth - (Optional) Enable or disable the re-authentication mechanism for a specific port.
disable - Disable the re-authentication mechanism for a specific port.
Format
config 802.1x auth_parameter ports [<portlist> | all] [default | {direction [both | in] |
port_control [force_unauth | auto | force_auth] | quiet_period <sec 0-65535> | tx_period
<sec 1-65535> | supp_timeout <sec 1-65535> | server_timeout <sec 1-65535> | max_req
<value 1-10> | reauth_period <sec 1-65535> | max_users [<v alue 1-448> | no_limit] |
enable_reauth [enable | disable]}(1)]
Parameters
both - For bidirectional access control.
by setting the parameter of port_control to be force_authorized or force_unauthorized.
Besides, the controlled port will reflect the outcome of authentication if port_control is auto.
force_auth - The port transmits and receives normal traffic without 802.1X-based
authentication of the client.
auto - The port begins in the unauthorized state, and relays authentication messages between
the client and the authentication server.
force_unauth - The port will remain in the unauthorized state, ignoring all attempts by the
and can be any value from 0 to 65535.
can be any value from 1 to 65535.
supplicant. Its default value is 30 s and can be any value from 1 to 65535.
authentication server. Its default value is 30 and can be any value from 1 to 65535.
will retransmit an EAP Request packet to the supplicant. Its default value is 2 and can be any
number from 1 to 10.
authentication timer. The default value is 3600.
<value 1-448> - The maximum users value must be between 1 and 448.
enable - Enable the re-authentication mechanism for a specific port.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
40
Page 46
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# config 802.1x auth_parameter ports 1-20 direction both
DGS-3620-28PC:admin#
enable - The authorization attributes such as VLAN, 802.1p default priority, and ACL assigned by
state is enabled.
disable - The authorization attributes assigned by the RADUIS server will not be accepted.
DGS-3620-28PC:admin#config 802.1x authorization attributes radius enable
DGS-3620-28PC:admin#
Example
To configure the parameters that control the operation of the authenticator associated with a port:
Command: config 802.1x auth_parameter ports 1-20 direction both
Success.
3-12 config 802.1x authorization attributes radius
Description
This command is used to enable or disable the acceptation of an authorized configuration. (To
configure that attributes, regarding VLAN, 802.1p, ACL and Ingress/Egress Bandwidth, please
refer to the Appendix section at the end of this document.)
Format
config 802.1x authorization attributes radius [enable | disable]
Parameters
the RADUIS server will be accepted if the global authorization status is enabled. The default
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the 802.1X state of acceptation of an authorized configuration:
Command: config 802.1x authorization attributes radius enable
Success.
3-13 config 802.1x init
Description
This command is used to initialize the authentication state machine of some or all.
41
Page 47
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
port_based ports - Used to configure authentication in port-based mode.
all - Specifies to configure all ports.
mac_based ports - To configure authentication in host-based 802.1X mode.
all - Specifies to configure all ports.
mac_address - (Option al) Specif ies the MAC address of the host.
<macaddr> - Enter the MAC address here.
DGS-3620-28PC:admin# config 802.1x init port_based ports all
DGS-3620-28PC:admin#
<value 1-448> - Enter the maximum number of users.
no_limit - Specifies an unlimited number of users.
Format
config 802.1x init [port_based p o rts [<portlist> | all] | mac_based ports [<portlist> | all ]
{mac_address <macaddr >}]
Parameters
<portlist> - Enter a range of ports to be configured.
<portlist> - Enter a range of ports to be configured.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To initialize the authentication state machine of some or all:
Command: config 802.1x init port_based ports all
Success.
3-14 config 802.1x max_users
Description
This command is used to configure the 802.1X maximum number of users of the system.
Format
config 802.1x max_users [<value 1-448> | no_limit]
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the 820.1X maximum numbers of the system:
42
Page 48
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# config 802.1x max_users 2
DGS-3620-28PC:admin#
port_based ports - The switch passes data based on its authenticated port.
all - Specifies to configure all ports.
mac_based ports - The switch passes data based on the MAC address of authenticated
all - Specifies to configure all ports.
mac_address - (Option al) Specif ies the MAC address of the authenticated RADIUS client.
<macaddr> - Enter the MAC address here.
DGS-3620-28PC:admin# config 802.1x reauth port_based ports all
DGS-3620-28PC:admin#
Command: config 802.1x max_users 2
Success.
3-15 config 802.1x reaut h
Description
This command is used to reauthenticate the device connected with the port. During the
reauthentication period, the port status remains authorized until failed reauthentication.
Format
config 802.1x reauth [port_based ports [<portlist> | all] |mac_based ports [<portlist> | all]
{mac_address <macaddr >}]
Parameters
<portlist> - Enter a range of ports to be configured.
RADIUS client.
<portlist> - Enter a range of ports to be configured.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To reauthenticate the device connected with the port:
Command: config 802.1x reauth port_based ports all
Success.
3-16 create 802.1x guest_vlan
Description
This command is used to assign a static VLAN to be a guest VLAN. The specific VLAN which is
assigned to a guest VLAN must already exist. The specific VLAN which is assigned to the guest
VLAN can’t be deleted.
43
Page 49
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<vlan_name 32> - Enter the static VLAN to be a guest VLAN.
DGS-3620-28PC:admin# create 802.1x guest_vlan guestVLAN
DGS-3620-28PC:admin#
<vlan_name 32> - Enter the guest VLAN name.
DGS-3620-28PC:admin# delete 802.1x guest_vlan guestVLAN
DGS-3620-28PC:admin#
Format
create 802.1x guest_vlan <vlan_name 32>
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To assign a static VLAN to be a guest VLAN:
Command: create 802.1x guest_vlan guestVLAN
Success.
3-17 delete 802.1x guest_vlan
Description
This command is used to delete a guest VLAN setting, but not to delete the static VLAN itself.
Format
delete 802.1x guest_vlan <vlan_name 32>
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To delete a guest VLAN configuration:
Command: delete 802.1x guest_vlan guestVLAN
Success.
44
Page 50
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<portlist> - Enter a range of ports to be configured.
all - Specifies to configure all ports.
state - Specifies the guest VLAN port state of the configured ports.
disable - Remove from guest VLAN.
DGS-3620-28PC:admin# config 802.1x guest_vlan ports 1-8 state enable
DGS-3620-28PC:admin#
3-18 config 802.1x guest_ vlan ports
Description
This command is used to configure a guest VLAN setting.
Format
config 802.1x guest_vlan ports [<po rtlist> | all] state [enable | disable]
Parameters
enable - Join the guest VLAN.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure a guest VLAN setting for ports 1 to 8:
Command: config 802.1x guest_vlan ports 1-8 state enable
Warning, The ports are moved to Guest VLAN.
Success.
3-19 show 802.1x guest _ vlan
Description
This command is used to display guest VLAN information.
Format
show 802.1x guest_vlan
Parameters
None.
45
Page 51
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show 802.1x guest_vlan
DGS-3620-28PC:admin#
<server_index 1-3> - Enter the RADIUS server index.
<server_ip> - Enter the IP address of the RADIUS server.
<ipv6add> - Specifies the IPv6 address used.
key - Specifies the key pre-negotiated between switch and the RADIUS server. It is used to
<passwd 32> - The maximum length of the password is 32 characters long.
encryption_key - (Optional) Specifies the key pre-negotiated between the switch and the
<password 56> - Enter the enryption key.
default - Sets the auth_port to be 1812 and acct_port to be 1813.
auth_port - Specifies the UDP port number which is used to transmit RADIUS authentication
<udp_port_number 1-65535> - The authentication port value must be between 1 and 65535.
acct_port - Specifies the UDP port number which is used to transmit RADIUS accounting
65535.
timeout - Specifies the time, in seconds ,for waiting server reply. The default value is 5 seconds.
<int 1-255> - The timeout value must be between 1 and 255.
retransmit - Specifies the count for re-transmit. The default value is 2.
Restrictions
None.
Example
To display guest VLAN information:
Command: show 802.1x guest_vlan
Guest Vlan Setting
----------------------------------------------------------Guest vlan : guest
Enable guest vlan ports : 1-10
3-20 config radius add
Description
This command is used to add a new RADIUS server. The server with a lower index has higher
authenticative priorit y.
Format
config radius add <server_index 1-3> [<server_ip> |<ipv6addr>] [key <password 32> |
encryption_key <password 56>] [default | {auth_port <udp_port_number 1-65535> |
acct_port <udp_port_number 1-65535> | timeout <sec 1-255> | retransmit <int 1-20>}]
Parameters
encrypt user’s authentication data before being transmitted over the Internet. The maximum
length of the key is 32.
RADIUS server. It is used to encrypt the user’s authentication data before being transmitted
over the Internet.
data between the switch and the RADIUS server.The range is 1 to 65535.
statistics between the switch and the RADIUS server. The range is 1 to 65535.
<udp_port_number 1-65535> - The accounting statistics value must be between 1 and
46
Page 52
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<int 1-20> - The re-transmit value must be between 1 and 20.
DGS-3620-28PC:admin#config radius add 1 10.48.74.121 key dlink default
DGS-3620-28PC:admin#
enable - Specifies to enable the sending of 802.1X traps.
disable - Specifies to disable the sending of 802.1X traps.
DGS-3620-28PC:admin# config 802.1x trap state enable
DGS-3620-28PC:admin#
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To add a new RADIUS server:
Command: config radius add 1 10.48.74.121 key dlink default
Success.
3-21 config 802.1x trap state
Description
This command is used to enable or disable the sending of 802.1X traps.
Format
config 802.1x trap state [enable | disable]
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
This example shows how to enable the trap state for 802.1X.
Command: config 802.1x trap state enable
Success.
3-22 config radius delet e
Description
This command is used to delete a RADIUS server.
47
Page 53
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<server_index 1-3> - Enter the RADIUS server index. The range is from 1 to 3.
DGS-3620-28PC:admin#config radius delete 1
DGS-3620-28PC:admin#
<server_index 1-3> - Enter the RADIUS server index.
ipaddress - Specifies the IP address of the RADIUS server.
<ipv6addr> - Enter the IPv6 address here.
key - Specifies the key pre-negotiated between the switch and the RADIUS server. It is used to
maximum length of the key is 32.
encryption_key - (Optional) Specifies the key pre-negotiated between the switch and the
<password 56> - Enter the enryption key.
auth_port - Specifies the UDP port number which is used to transmit RADIUS authentication
data between the switch and the RADIUS server. The default is 1812.
Format
config radius delete <server_index 1-3>
Parameters
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To delete a RADIUS server:
Command: config radius delete 1
Success.
3-23 config radius
Description
This command is used to configure a RADIUS server.
Format
config radius <server_index 1-3> {ipaddress [<server_ip> |<ipv6addr>] | [key <password
32> | encryption_key <password 56>] | auth_port [<udp_port_number 1-65535> | default] |
acct_port [<udp_port_number 1-65535> | d efault] | timeout [<sec 1-255> | default] |
retransmit [<int 1-20> | default]}
Parameters
<server_ip> - Enter the RADIUS server IP address here.
encrypt user’s authentication data before being transmitted over the Internet. The maximum
length of the key is 32.
<passwd 32> - Enter the key pre-negotiated between the switch and the RADIUS server. It is
used to encrypt user’s authentication data before being transmitted over the Internet. The
RADIUS server. It is used to encrypt the user’s authentication data before being transmitted
over the Internet.
48
Page 54
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<udp_port_number 1-65535> - The authentication port value must be between 1 and 65535.
default - Specifies to use the default value.
acct_port - Specifies the UDP port number which is used to transmit RADIUS accounting
default - Specifies to use the default value.
timeout - Specifies the time in seconds for waiting for a server reply. The default value is 5
default - Specifies to use the default value.
retransmit - Specifies the count for re-transmission. The default value is 2.
default - Specifies to use the default value.
DGS-3620-28PC:admin#config radius 1 ipaddress 10.48.74.121 key dlink
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show radius
statistics between the switch and the RADIUS server. The default is 1813.
<udp_port_number 1-65535> - The accounting statistics value must be between 1 and
65535.
seconds.
<int 1-255> - Enter the time in seconds for waiting for a server reply. The timeout value must
be between 1 and 255. The default value is 5 seconds.
<int 1-20> - The re-transmit value must be between 1 and 20.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure a RADIUS server:
Command: config radius 1 ipaddress 10.48.74.121 key dlink
Success.
3-24 show radius
Description
This command is used to display RADIUS server configurations.
Format
show radius
Parameters
None.
Restrictions
None.
Example
To display RADIUS server configurations:
49
Page 55
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Command: show radius
DGS-3620-28PC:admin#
ports - (Optional) Specifies a range of ports to be displayed.
<portlist> - Enter a range of ports to be displayed.
DGS-3620-28PC:admin# show auth_statistics ports 3
EapolRespFramesRx 0
Index 1
IP Address : 192.168.69.1
Auth-Port : 1812
Acct-Port : 1813
Timeout : 5
Retransmit : 2
Key : 123456
Total Entries : 1
3-25 show auth_statistics
Description
This command is used to display authenticator statistics information
Format
show auth_statistics {ports <por tlist>}
Parameters
Restrictions
None.
Example
To display authenticator statistics information for port 3:
Command: show auth_statistics ports 3
Auth VID :100
MAC Address :00-00-00-00-00-03
Port number : 3
EapolFramesRx 0
EapolFramesTx 6
EapolStartFramesRx 0
EapolReqIdFramesTx 6
EapolLogoffFramesRx 0
EapolReqFramesTx 0
EapolRespIdFramesRx 0
50
Page 56
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
InvalidEapolFramesRx 0
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
ports - (Optional) Specifies a range of ports to be displayed.
<portlist> - Enter a range of ports to be displayed.
DGS-3620-28PC:admin# show auth_diagnostics ports 3
BackendOtherRequestsToSupplicant 0
EapLengthErrorFramesRx 0
LastEapolFrameVersion 0
LastEapolFrameSource 00-00-00-00-00-03
3-26 show auth_diagno s tics
Description
This command is used to display authenticator diagnostics information.
Format
show auth_diagnostics {ports <portlist>}
Parameters
Restrictions
None.
Example
To display authenticator diagnostics information for port 3:
Command: show auth_diagnostics ports 3
Auth VID 100
MAC Address 00-00-00-00-00-03
Port number : 1
EntersConnecting 20
EapLogoffsWhileConnecting 0
EntersAuthenticating 0
SuccessWhileAuthenticating 0
TimeoutsWhileAuthenticating 0
FailWhileAuthenticating 0
ReauthsWhileAuthenticating 0
EapStartsWhileAuthenticating 0
EapLogoffWhileAuthenticating 0
ReauthsWhileAuthenticated 0
EapStartsWhileAuthenticated 0
EapLogoffWhileAuthenticated 0
BackendResponses 0
BackendAccessChallenges 0
51
Page 57
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
BackendNonNakResponsesFromSupplicant 0
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
ports - (Optional) Specifies a range of ports to be displayed.
<portlist> - Enter a range of ports to be displayed.
DGS-3620-28PC:admin# show auth_session_statistics ports 3
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
BackendAuthSuccesses 0
BackendAuthFails 0
3-27 show auth_session_statistics
Description
This command is used to display authenticator session statistics information.
Format
show auth_session_stat istics {p ort s <portl ist >}
Parameters
Restrictions
None.
Example
To display authenticator session statistics information for port 1:
Command: show auth_session_statistics ports 3
Auth VID : 100
MAC Address : 00-00-00-00-00-03
Port number : 3
SessionOctetsRx 0
SessionOctetsTx 0
SessionFramesRx 0
SessionFramesTx 0
SessionId
SessionAuthenticMethod Remote Authentication Server
SessionTime 0
SessionTerminateCause SupplicantLogoff
SessionUserName
3-28 show auth_client
Description
This command is used to display authentication client information.
52
Page 58
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# show auth_client
radiusAuthServerAddress 0.0.0.0
Format
show auth_client
Parameters
None.
Restrictions
None.
Example
To display authentication client information:
Command: show auth_client
radiusAuthClient ==>
radiusAuthClientInvalidServerAddresses 0
radiusAuthClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAuthServerIndex :1
radiusAuthServerAddress 0.0.0.0
radiusAuthClientServerPortNumber X
radiusAuthClientRoundTripTime 0
radiusAuthClientAccessRequests 0
radiusAuthClientAccessRetransmissions 0
radiusAuthClientAccessAccepts 0
radiusAuthClientAccessRejects 0
radiusAuthClientAccessChallenges 0
radiusAuthClientMalformedAccessResponses 0
radiusAuthClientBadAuthenticators 0
radiusAuthClientPendingRequests 0
radiusAuthClientTimeouts 0
radiusAuthClientUnknownTypes 0
radiusAuthClientPacketsDropped 0
radiusAuthClient ==>
radiusAuthClientInvalidServerAddresses 0
radiusAuthClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAuthServerIndex :2
53
Page 59
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
radiusAuthClientServerPortNumber X
DGS-3620-28PC:admin#
radiusAuthClientRoundTripTime 0
radiusAuthClientAccessRequests 0
radiusAuthClientAccessRetransmissions 0
radiusAuthClientAccessAccepts 0
radiusAuthClientAccessRejects 0
radiusAuthClientAccessChallenges 0
radiusAuthClientMalformedAccessResponses 0
radiusAuthClientBadAuthenticators 0
radiusAuthClientPendingRequests 0
radiusAuthClientTimeouts 0
radiusAuthClientUnknownTypes 0
radiusAuthClientPacketsDropped 0
radiusAuthClient ==>
radiusAuthClientInvalidServerAddresses 0
radiusAuthClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAuthServerIndex :3
radiusAuthServerAddress 0.0.0.0
radiusAuthClientServerPortNumber X
radiusAuthClientRoundTripTime 0
radiusAuthClientAccessRequests 0
radiusAuthClientAccessRetransmissions 0
radiusAuthClientAccessAccepts 0
radiusAuthClientAccessRejects 0
radiusAuthClientAccessChallenges 0
radiusAuthClientMalformedAccessResponses 0
radiusAuthClientBadAuthenticators 0
radiusAuthClientPendingRequests 0
radiusAuthClientTimeouts 0
radiusAuthClientUnknownTypes 0
radiusAuthClientPacketsDropped 0
3-29 show acct_client
Description
This command is used to display account client information
Format
show acct_client
Parameters
None.
54
Page 60
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# show acct_client
radiusAccClientPacketsDropped 0
Restrictions
None.
Example
To display account client information:
Command: show acct_client
radiusAcctClient ==>
radiusAcctClientInvalidServerAddresses 0
radiusAcctClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAccServerIndex : 1
radiusAccServerAddress 0.0.0.0
radiusAccClientServerPortNumber X
radiusAccClientRoundTripTime 0
radiusAccClientRequests 0
radiusAccClientRetransmissions 0
radiusAccClientResponses 0
radiusAccClientMalformedResponses 0
radiusAccClientBadAuthenticators 0
radiusAccClientPendingRequests 0
radiusAccClientTimeouts 0
radiusAccClientUnknownTypes 0
radiusAccClientPacketsDropped 0
radiusAcctClient ==>
radiusAcctClientInvalidServerAddresses 0
radiusAcctClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAccServerIndex : 2
radiusAccServerAddress 0.0.0.0
radiusAccClientServerPortNumber X
radiusAccClientRoundTripTime 0
radiusAccClientRequests 0
radiusAccClientRetransmissions 0
radiusAccClientResponses 0
radiusAccClientMalformedResponses 0
radiusAccClientBadAuthenticators 0
radiusAccClientPendingRequests 0
radiusAccClientTimeouts 0
radiusAccClientUnknownTypes 0
55
Page 61
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#
radiusAcctClient ==>
radiusAcctClientInvalidServerAddresses 0
radiusAcctClientIdentifier D-Link
radiusAuthServerEntry ==>
radiusAccServerIndex : 3
radiusAccServerAddress 0.0.0.0
radiusAccClientServerPortNumber X
radiusAccClientRoundTripTime 0
radiusAccClientRequests 0
radiusAccClientRetransmissions 0
radiusAccClientResponses 0
radiusAccClientMalformedResponses 0
radiusAccClientBadAuthenticators 0
radiusAccClientPendingRequests 0
radiusAccClientTimeouts 0
radiusAccClientUnknownTypes 0
radiusAccClientPacketsDropped 0
56
Page 62
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
enable authen_policy
disable authen_policy
show authen_policy
enable authen_policy_encryption
disable authen_policy_encryption
create authen_login method_list_name <string 15>
config authen_login [default | method_list_name <string 15>] method {tacacs | xtacacs | tacacs+
| radius | server_group <string 15> | local | none}(1)
delete authen_login method_list_name <string 15>
show authen_login [default | method_list_name <string 15> | all]
create authen_enable method_list_name <string 15>
config authen_enable [default | method_list_name <string 15>] method {tacacs | xtacacs |
tacacs+ | radius | server_group <string 15> | local_enable | none}(1)
delete authen_enable method_list_name <string 15>
show authen_enable [default | method_list_name <string 15> | all]
config authen application [console | telnet | ssh | http | all] [login | enable] [default |
method_list_name <s tr ing 15> ]
show authen application
create authen server_group <string 15>
config authen server_group [tacacs | xtacacs | tacacs+ | radius | <string 15>] [add | delete]
server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
delete authen server_group <string 15>
show authen server_group {<string 15>}
create authen server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius] {port <int 1-
255> | retransmit <int 1-20>}
config authen server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius] {port <int 1-
255> | retransmit <int 1-20>}(1)
delete authen server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
show authen server_host
config authen parameter response_ti m eout <int 0-255>
config authen parameter attempt <int 1-255>
show authen parameter
enable admin
config admin local_enable {encrypt [plain_text | sha_1] <password>}
create aaa server_group <string 15>
config aaa server_group [tacacs | xtacacs | tacacs+ | radius | group_name <string 15>] [add |
delete] server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
delete aaa server_group <string 15>
delete aaa server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
show aaa
show aaa server_group {<string 15>}
show aaa server_host
enable aaa_server_pass word_encryption
disable aaa_server_password_encryption
config accounting [default | method_list_name <string 15>] method {tacacs+ | radius |
Chapter 4 Access Authenticat ion
Control (AAC)
Commands
65535> | [key [<key_string 254> | none] | encr yption_key <key_string 344>] | timeout <int 1-
65535> | [key [<key_string 254> | none] | encr yption_key <key_string 344>] | timeout <int 1-
57
Page 63
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
server_group <string 15> | none}
config accounting service [network | shell | system] state [enable {[radius_only |
method_list_name <string 15> | default_method_lis t]} | disab le]
config accounting service command {administrator | operator | power_user | user}
[method_list_name <string> | none]
create accounting method_lis t_name <string 15>
delete accounting method_list_ n ame <string 15 >
show accounting [default | method_list_name <string 15> | all]
show accounting service
create radius server_host <ipaddr> {auth _port < int 1-65535> | acct_port <int 1-65535> | [key
retransmit <int 1-20>}
config radius server_host <ipaddr> {auth_port <int 1-65535> | acct_port <int 1-65535> | [key
retransmit <int 1-20>}
config radius source_ipif [<ipif_name 12> {<ipaddr> | <ipv6addr>} | none]
show radius source_ipif
create tacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit <int 1-
20>}
config tacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit <int 1-
20>}
create tacacs+ server_host <ipaddr> {port <int 1-65535> | [key [<key_string 254> | none] |
encryption_key <key_string 344>] | timeout <int 1-255>}
config tacacs+ server_host <ipaddr> {port <int 1-65535> | [key [<key_string 254> | none] |
encryption_key <key_string 344>] | timeout <int 1-255>}
create xtacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit <int 1-
20>}
config xtacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit <int 1-
20>}
config tacacs source_ipif [<ipif_name 12> {<ipaddr>} | none]
show tacacs source_ipif
[<key_string 254> | none] | encryption_key <key_string 344>] | timeout <int 1-255> |
[<key_string 254> | none] | encryptio n_k ey <key_string 344>] | timeout <int 1-255> |
The TACACS / XTACACS / TACACS+ / RADIUS commands allows secure access to the Switch
using the TACACS / XTACACS / TACACS+ / RADIUS protocols. When a user logs in to the
Switch or tries to access the administrator level privilege, he or she is prompted for a password. If
TACACS / XTACACS / TACACS+ / RADIUS authentication is enabled on the Switch, it will contact
a TACACS / XTACACS / TACACS+ / RADIUS server to verify the user. If the user is verified, he or
she is granted access to the Switch.
There are currently three versions of the TACACS security protocol, each a separate entity. The
Switch’s software supports the following versions of TACACS:
1. TACACS (Terminal Access Controller Access Control System) —Provides password
checking and authentication, and notification of user actions for security purposes utilizing
via one or more centralized TACACS servers, utilizing the UDP protocol for packet
transmission.
2. Extended TACACS (XTACACS) — An extension of the TACACS protocol with the ability
to provide more types of authentication requests and more types of response codes than
TACACS. This protocol also uses UDP to transmit packets.
3. TACACS+ (Terminal Access Controller Access Control System plus) — Provides
detailed access control for authentication for network devices. TACACS+ is facilitated
through Authentication commands via one or more centralized servers. The TACACS+
protocol encrypts all traffic between the Switch and the TACACS+ daemon, using the TCP
protocol to ensure reliable delivery.
58
Page 64
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Note: User granted access to the Switch will be granted normal user privileges on the
Note: TACACS, XTACACS and TACACS+ are separate entities and are not compatible.
The Switch also supports the RADIUS protocol for authentication using the Access Authentication
Control commands. RADIUS or Remote Authentication Dial In User Server also uses a remote
server for authentication and can be responsible for receiving user connection requests,
authenticating the user and returning all configuration information necessary for the client to deliver
service through the user. RADIUS may be facilitated on this Switch using the commands listed in
this section.
In order for the TACACS / XTACACS / TACACS+ / RADIUS security function to work properly, a
TACACS / XTACACS / TACACS+ / RADIUS server must be configured on a device other than the
Switch, called a server host and it must include usernames and passwords for authentication.
When the user is prompted by the Switch to enter usernames and passwords for authentication,
the Switch contacts the TACACS / XTACACS / TACACS+ / RADIUS server to verify, and the
server will respond with one of three messages:
The server verifies the username and password, and the user is granted normal user privileges on
the Switch. The server will not accept the username and password and the user is denied access
to the Switch.
The server doesn’t respond to the verification query. At this point, the Switch receives the timeout
from the server and then moves to the next method of verification configured in the method list.
The Switch has four built-in server groups, one for each of the TACACS, XTACACS, TACACS+
and RADIUS protocols. These built-in server groups are used to authenticate users trying to
access the Switch. The users will set server hosts in a preferable order in the built-in server group
and when a user tries to gain access to the Switch, the Switch will ask the first server host for
authentication. If no authentication is made, the second server host in the list will be queried, and
so on. The built-in server group can only have hosts that are running the specified protocol. For
example, the TACACS server group can only have TACACS server hosts.
The administrator for the Switch may set up five different authentication techniques per userdefined method list (TACACS / XTACACS / TACACS+ / RADIUS / local / none) for authentication.
These techniques will be listed in an order preferable, and defined by the user for normal user
authentication on the Switch, and may contain up to eight authentication techniques. When a user
attempts to access the Switch, the Switch will select the first technique listed for authentication. If
the first technique goes through its server hosts and no authentication is returned, the Switch will
then go to the next technique listed in the server group for authentication, until the authentication
has been verified or denied, or the list is exhausted.
Switch. To gain access to admin level privileges, the user must enter the enable
admin command and then enter a password, which was previously configured by
the administrator of the Switch.
The Switch and the server must be configured exactly the same, using the same
protocol. (For example, if the Switch is set up for TACACS authentication, so must
be the host server.)
4-1 enable authen_policy
Description
This command is used to enable system access authentication policy. When enabled, the device
will adopt the login authentication method list to authenticate the user for login, and adopt the
enable authentication mothod list to authenticate the enable password for promoting the user‘s
privilege to Administrator leve l.
59
Page 65
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable authen_policy
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#disable authen_policy
Format
enable authen_policy
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To enable system access authentication policy:
Command: enable authen_policy
Success.
4-2 disable authen_policy
Description
This command is used to disable system access authentication policy. When authentication is
disabled, the device will adopt the local user account database to authenticate the user for login,
and adopt the local enable password to authen tic at e the enable password for promoting the user‘s
privilege to Administrator leve l.
Format
disable authen_policy
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To disable system access authentication policy:
Command: disable authen_policy
60
Page 66
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Success.
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show authen_policy
DGS-3620-28PC:admin#
4-3 show authen_policy
Description
This command is used to display whether system access authentication policy is enabled or
disabled.
Format
show authen_policy
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To display system access authentication policy:
Command: show authen_policy
Authentication Policy : Disabled
Authentication Policy Encryption: Disabled
4-4 enable authen_policy_encry ption
Description
This command is used to enable the authentication policy encryption. When enabled, TACACS+
and RADIUS key will be in the encrypted form.
Format
enable authen_policy_encryption
Parameters
None.
61
Page 67
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable authen_policy_encryption
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#disable authen_policy_encryption
DGS-3620-28PC:admin#
Restrictions
Only Administrator-level users can issue this command.
Example
To enable the authentication policy encryption:
Command: enable authen_policy_encryption
Success.
4-5 disable authen_policy_encryption
Description
This command is used to disable the authentication policy encryption. When disabled, TACACS+
and RADIUS key will be in the plain text form.
Format
disable authen_policy_encryption
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To disable the authentication policy encryption:
Command: disable authen_policy_encryption
Success.
4-6 create authen_login method_list_name
Description
This command is used to create a user-defined method list of authentication methods for user
login. The maximum supported number of the login method lists is eight.
62
Page 68
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<string 15> - Enter the user-defined method list name.
DGS-3620-28PC:admin#create authen_login method_list_name login_list_1
DGS-3620-28PC:admin#
default – Specify the default method list of authentication methods.
method_list_name - Specifies the user-defined method list of authentication methods.
name can be up to 15 characters long.
method - Choose the desired authentication method:
Format
create authen_login method_list_name <string 15>
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To create a user-defined method list for user login:
Command: create authen_login method_list_name login_list_1
Success.
4-7 config authen_login
Description
This command is used to configure a user-defined or default method list of authentication methods
for user login. The sequence of methods will affect the authentication result. For example, if the
sequence is TACACS+ first, then TACACS and local, when a user trys to login, the authentication
request will be sent to the first server host in the TACACS+ built-in server group. If the first server
host in the TACACS+ group is missing, the authentication request will be sent to the second server
host in the TACACS+ group, and so on. If all server hosts in the TACACS+ group are missing, the
authentication request will be sent to the first server host in the TACACS group. If all server hosts
in a TACACS group are missing, the local account database in the device is used to authenticate
this user. When a user logs in to the device successfully while using methods like
TACACS/XTACACS/TACACS+/RADIUS built-in or user-defined server groups or none, the “user”
privilege level is assigned only. If a user wants to get admin privilege level, the user must use the
“enable admin” command to promote his privilege level. But when the local method is used, the
privilege level will depend on this account privilege level stored in the local device.
Format
config authen_login [default | method_list_name <string 15>] method {tacacs | xtacacs |
tacacs+ | radius | server_group <string 15> | local | none}(1)
Parameters
<string 15> - Enter the user-defined method list of authentication methods. The method list
63
Page 69
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
tacacs - Specifies authentication by the built-in server group TACACS.
none - Specifies no authenticati on.
DGS-3620-28PC:admin#config authen_login method_list_name login_list_1 method
DGS-3620-28PC:admin#
<string 15> - Enter the user-defined method list name.
DGS-3620-28PC:admin#delete authen_login method_list_name login_list_1
xtacacs - Specifies authentication by the built-in server group XTACACS.
tacacs+ - Specifies authentication by the built-in server group TACACS+.
radius - Specifies authentication by the built-in server group RADIUS.
server_group - Specifies authentication by the user-defined server group.
<string 15> - Enter authentication by the user-defined server group. The server group
value can be up to 15 characters long.
local - Specifies authentication by local user account database in the device.
Restrictions
Only Administrator-level users can issue this command.
Example
To configure a user-defined method list for user login:
tacacs+ tacacs local
Command: config authen_login method_list_name login_list_1 method tacacs+
tacacs local
Success.
4-8 delete authen_login method_list_name
Description
This command is used to delete a user-defined method list of authentication methods for user login.
Format
delete authen_login method_list_name <string 15>
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To delete a user-defined method list for user login:
Command: delete authen_login method_list_name login_list_1
Success.
64
Page 70
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#
default – Specify to display the default method list for user login.
method_list_name - Specifies the user-defined method list for user login.
up to 15 characters long.
all – Specify to display all method lists for user login.
DGS-3620-28PC:admin#show authen_login method_list_name login_list_1
DGS-3620-28PC:admin#
4-9 show authen_login
Description
This command is used to display the method list of authentication methods for user login.
Format
show authen_login [default | method_list_name <string 15> | all]
Parameters
<string 15> - Enter the user-defined method list for user login. The method list name can be
Restrictions
Only Administrator-level users can issue this command.
Example
To display a user-defined method list for user login:
Command: show authen_login method_list_name login_list_1
Method List Name Priority Method Name Comment
---------------- -------- --------------- -----------------login_list_1 1 tacacs+ Built-in Group
2 tacacs Built-in Group
3 mix_1 User-defined Group
4 local Keyword
4-10 create authen_enable method_list_name
Description
This command is used to create a user-defined method list of authentication methods for
promoting a user's privilege to Admin level. The maximum supported number of the enable method
lists is eight.
Format
create authen_enable method_list_name <string 15>
65
Page 71
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<string 15> - Enter the user-defined method list name.
DGS-3620-28PC:admin#create authen_enable method_list_name enable_list_1
DGS-3620-28PC:admin#
default - Specifies the default method list of authentication methods.
method_list_name - Specifies the user-defined method list of authentication methods.
name can be up to 15 characters long.
method - Choose the desired authentication method:
value can be up to 15 characters long.
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To create a user-defined method list for promoting a user's privilege to Admin level:
Command: create authen_enable method_list_name enable_list_1
Success.
4-11 config authen_ena ble
Description
This command is used to configure a user-defined or default method list of authentication methods
for promoting a user's privilege to Admin level. The sequence of methods will effect the
authencation result. For example, if the sequence is TACACS+ first, then TACACS and
local_enable, when a user tries to promote a user's privilege to Admin level, the authentication
request will be sent to the first server host in the TACACS+ built-in server group. If the first server
host in the TACACS+ group is missing, the authentication request will be sent to the second server
host in the TACACS+ group, and so on. If all server hosts in the TACACS+ group are missing, the
authentication request will be sent to the first server host in the TACACS group. If all server hosts
in the TACACS group are missing, the local enable password in the device is used to authenticate
this user’s password. The local enable password in the device can be configured by the CLI
command config admin local_enable.
Format
config authen_enable [default | method_list_name <string 15>] method {tacacs | xtacacs |
tacacs+ | radius | server_group <string 15> | local_enable | none}(1)
Parameters
<string 15> - Enter the user-defined method list of authentication methods. The method list
tacacs - Specifies authentication by the built-in server group TACACS.
xtacacs - Specifies authentication by the built-in server group XTACACS.
tacacs+ - Specifies authentication by the built-in server group TACACS+.
radius - Specifies authentication by the built-in server group RADIUS.
server_group - Specifies authentication by the user-defined server group.
<string 15> - Enter authentication by the user-defined server group. The server group
66
Page 72
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
local_enable - Specifies authentication by local enable password in the device.
none - Specifies no authenticati on.
DGS-3620-28PC:admin#config authen_enable method_list_name enable_list_1 method
DGS-3620-28PC:admin#
<string 15> - Enter the user-defined method list name.
DGS-3620-28PC:admin#delete authen_enable method_list_name enable_list_1
DGS-3620-28PC:admin#
Restrictions
Only Administrator-level users can issue this command.
Example
To configure a user-defined method list for promoting a user's privilege to Admin level:
tacacs+ tacacs local_enable
Command: config authen_ enable method_list_name enable_list_1 method tacacs+
tacacs local_enable
Success.
4-12 delete authen_enable method_list_name
Description
This command is used to delete a user-defined method list of authentication methods for
promoting a user's privilege to Administrator level.
Format
delete authen_enable method_list_name <string 15>
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To delete a user-defined method list for promoting a user's privilege to Admin level:
Command: delete authen_enable method_list_name enable_list_1
Success.
67
Page 73
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
default - Specifies to display the default method list for promoting a user's privilege to
Administrator level.
method_list_name - Specifies the user-defined method list for promoting a user's privilege to
Administrator level . The method list name value can be up to 15 characters long.
all - Specifies to display all method lists for promoting a user's privilege to Administrator level.
DGS-3620-28PC:admin#show authen_enable all
DGS-3620-28PC:admin#
4-13 show authen_enabl e
Description
This command is used to display the method list of authentication methods for promoting a user's
privilege to Administrator leve l.
Format
show authen_enable [default | method_list_name <string 15> | all]
Parameters
Administrator level.
<string 15> - Enter the user-defined method list for a promoting a user's privilege to
Restrictions
Only Administrator-level users can issue this command.
Example
To display all method lists for promoting a user's privilege to Administrator level:
Command: show authen_enable all
Method List Name Priority Method Name Comment
---------------- -------- --------------- -----------------default 1 local_enable Keyword
enable_list_1 1 tacacs+ Built-in Group
2 tacacs Built-in Group
3 mix_1 User-defined Group
4 loca_enable Keyword
enable_list_2 1 tacacs+ Built-in Group
2 radius Built-in Group
Total Entries : 3
4-14 config authen appli cation
Description
This command is used to configure login or enable method list for all or the specified application.
68
Page 74
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
console - Specifies an application: console.
all - Specifies all applications: console, Telnet, SSH, and Web.
login - Specifies the method list of authentication methods for user login.
Administrator level.
default - Specifies the default method list.
to 15 characters long.
DGS-3620-28PC:admin#config authen application telnet login method_list_name
DGS-3620-28PC:admin#
Format
config authen application [console | telnet | ssh | http | all] [login | enable] [defaul t |
method_list_name <string 15>]
Parameters
telnet - Specifies an application: Telnet.
ssh - Specifies an application: SSH.
http - Specifies an application: Web.
enable - Specifies the method list of authentication methods for promoting user privilege to
method_list_name - Specifies the user-defined method list name.
<string 15> - Enter the user-defined method list name. The method list name value can be up
Restrictions
Only Administrator-level users can issue this command.
Example
To configure the login method list for Telnet:
login_list_1
Command: config authen application telnet login method_list_name login_list_1
Success.
4-15 show authen applicat ion
Description
This command is used to display the login/enable method list for all applications.
Format
show authen application
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
69
Page 75
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show authen application
DGS-3620-28PC:admin#
<string 15> - Enter the user-defined server group name.
DGS-3620-28PC:admin#create authen server_group mix_1
DGS-3620-28PC:admin#
Example
To display the login and enable method list for all applications:
Command: show authen application
Application Login Method List Enable Method List
----------- ----------------- -----------------Console default default
Telnet login_list_1 default
SSH default default
HTTP default default
4-16 create authen serv er_group
Description
This command is used to create a user-defined authentication server group. The maximum
supported number of server groups including built-in server groups is eight. Each group consists of
eight server hosts as maximum.
Format
create authen server_group <string 15>
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To create a user-defined authentication server group:
Command: create authen server_group mix_1
Success.
4-17 config authen server _ group
Description
This command is used to add or remove an authentication server host to or from the specified
server group. Built-in server group tacacs, xtacacs, tacacs+, and RADIUS accept the server host
with the same protocol only, but user-defined server group can accept server hosts with different
70
Page 76
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
tacacs - Specifies the built-in server group TACACS.
<string 15> - Enter a user-defined server group.
add - Specifies to add a server host to a server group.
delete - Specifies to remove a server host from a server group.
server_host - Specifies the server host’s IP address.
<ipaddr> - Enter the server host’s IP address.
protocol - Specifies the server host’s type of authentication protocol.
radius - Specifies the server host’s authentication protocol RADIUS.
DGS-3620-28PC:admin#config authen server_group mix_1 add server_host 10.1.1.222
DGS-3620-28PC:admin#
protocols. The server host must be created first by using the CLI command create authen
server_host.
Format
config authen server_group [tacacs | xtacacs | tacacs+ | radius | <string 15>] [add | delete]
server_host <ipaddr> protocol [tac acs | xtacacs | tacacs+ | radius]
Parameters
xtacacs - Specifies t he buil t-in server group XTACACS.
tacacs+ - Specifies the built-in server group TACACS+.
radius – Specify the built-in server group RADIUS.
tacacs - Specifies the server host’s authentication protocol TACACS.
xtacacs - Specifies the server host’s authentication protocol XTACACS.
tacacs+ - Specifies the server host’s authentication protocol TACACS+.
Restrictions
Only Administrator-level users can issue this command.
Example
To add an authentication server host to a server group:
protocol tacacs+
Command: config authen server_group mix_1 add server_host 10.1.1.222 protocol
tacacs+
Success.
4-18 delete authen server_group
Description
This command is used to delete a user-defined authentication server group.
Format
delete authen server_group <string 15>
71
Page 77
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<string 15> - Enter the user-defined server group name.
DGS-3620-28PC:admin#delete authen server_group mix_1
DGS-3620-28PC:admin#
<string 15> - (Optional) Specifies the built-in or user-defined server group name.
DGS-3620-28PC:admin#show authen server_group
Total Entries : 5
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To delete a user-defined authentication server group:
Command: delete authen server_group mix_1
Success.
4-19 show authen server_group
Description
This command is used to display the authentication server groups.
Format
show authen server_group {<stri n g 15>}
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To display all authentication server groups:
Command: show authen server_group
Group Name IP Address Protocol
--------------- --------------- -------mix_1 10.1.1.222 TACACS+
radius 10.1.1.224 RADIUS
tacacs 10.1.1.225 TACACS
tacacs+ 10.1.1.226 TACACS+
xtacacs 10.1.1.227 XTACACS
72
Page 78
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#
<ipaddr> - Enter the server host’s IP address.
protocol - Specifies the server host’s type of authentication protocol.
radius - Specifies the server host’s authentication protocol RADIUS.
port - (Optional) Specifies the port number of the authentication protocol for the server host. The
1812. The port number must be between 1 and 65535.
key - (Optional) Specif ies the key for TACACS+ and RADIUS authentication.
for TACACS and XTACACS.
encryption_key - (Optional) Specifies the encrypted form key string for TACACS+ and RADIUS
authentication.
timeout - (Optional) Specifies the time in seconds for waiting for a server reply. The default value
seconds. The timeout value must be between 1 and 255 seconds.
retransmit - (Optional) Specifies the count for re-transmit. This value is meaningless for
default value is 2. The re-transmit value must be between 1 and 20.
4-20 create authen serv er_host
Description
This command is used to create an authentication server host. When an authentication server host
is created, the IP address and protocol are the index. That means more than one authentication
protocol service can be run on the same physical host. The maximum supported number of server
hosts is 16.
Format
create authen server_host <ipaddr> p rotocol [tacacs | xtacacs | tacacs+ | radius] {port <int
1-65535> | [key [<key_string 254> | none] | en cryption_key <key_string 344>] | timeout <int
1-255> | retransmit <int 1-20>}
Parameters
tacacs - Specifies the server host’s authentication protocol TACACS.
xtacacs - Specifies the server host’s authentication protocol XTACACS.
tacacs+ - Specifies the server host’s authentication protocol TACACS+.
default value for TACACS/XTACACS/TACACS+ is 49. The default value for RADIUS is 1812.
<int 1-65535> - Enter the port number of the authentication protocol for the server host. The
default value for TACACS/XTACACS/TACACS+ is 49. The default value for RADIUS is
<key_string 254> - Enter the key for TACACS+ and RADIUS authenticaiton. If the value is
null, no encryption will apply. This value is meaningless for TACACS and XTACACS.
none - No encryption for TACACS+ and RADIUS authenticaiton. This value is meaningless
authentication. This value is meaningless for TACACS and XTACACS. The encryption
algorithm is based on DES.
<key_string 344> - Enter the encrypted form key string for TACACS+ and RADIUS
is 5 seconds.
<int 1-255> - Enter the time in seconds for waiting for a server reply. The default value is 5
TACACS+. The default value is 2.
<int 1-20> - Enter the count for re-transmit. This value is meaningless for TACACS+. The
Restrictions
Only Administrator-level users can issue this command.
73
Page 79
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#create authen server_host 10.1.1.222 protocol tacacs+ port
DGS-3620-28PC:admin#
<ipaddr> - Enter the server host’s IP address.
protocol - Specifies the server host’s type of authentication protocol.
radius - Specifies the server host’s authentication protocol RADIUS.
port - Specifies the port number of the authentication protocol for the server host. The default
1812. The port number must be between 1 and 65535.
key - Specifies the key for TACACS+ and RADIUS authentication.
meaningless for TACACS and XTACACS.
encryption_key - (Optional) Specifies the encrypted form key string for TACACS+ and RADIUS
authentication.
timeout - Specifies the time in seconds for waiting for a server reply. The default value is 5
seconds. The timeout value must be between 1 and 255 seconds.
retransmit - Specifies the count for re-transmit. This value is meaningless for TACACS+. The
default value is 2. The re-transmit value must be between 1 and 20.
Example
To create a TACACS+ authentication server host with a listening port number of 15555 and a
timeout value of 10 seconds:
15555 key "123" timeout 10
Command: create authen server_host 10.1.1.222 protocol tacacs+ port 15555 key
"123" timeout 10
Success.
4-21 config authen server _ hos t
Description
This command is used to configure an authentication server host.
Format
config authen server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius] {port <int
1-65535> | [key [<key_string 254> | none] | en cryption_key <key_string 344>] | timeout <int
1-255> | retransmit <int 1-20>}(1)
Parameters
tacacs - Specifies the server host’s authentication protocol TACACS.
xtacacs - Specifies the server host’s authentication protocol XTACACS.
tacacs+ - Specifies the server host’s authentication protocol TACACS+.
value for TACACS/XTACACS/TACACS+ is 49. The default value for RADIUS is 1812.
<int 1-65535> - Enter the port number of the authentication protocol for the server host. The
default value for TACACS/XTACACS/TACACS+ is 49. The default value for RADIUS is
<key_string 254> - Enter the key for TACACS+ and RADIUS authentication. If the value is
null, no encryption will apply. This value is meaningless for TACACS and XTACACS.
none - Specifies no encryption for TACACS+ and RADIUS authentication. This value is
authentication. This value is meaningless for TACACS and XTACACS. The encryption
algorithm is based on DES.
<key_string 344> - Enter the encrypted form key string for TACACS+ and RADIUS
seconds.
<int 1-255> - Enter the time in seconds for waiting for a server reply. The default value is 5
default value is 2.
<int 1-20> - Enter the count for re-transmit. This value is meaningless for TACACS+. The
74
Page 80
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config authen server_host 10.1.1.222 protocol tacacs+ key
DGS-3620-28PC:admin#
<ipaddr> - Enter the server host’s IP address.
protocol - Specifies the server host’s type of authentication protocol.
radius - Specifies the server host’s authentication protocol RADIUS.
DGS-3620-28PC:admin#delete authen server_host 10.1.1.222 protocol tacacs+
DGS-3620-28PC:admin#
Restrictions
Only Administrator-level users can issue this command.
Example
To configure a TACACS+ authentication server host’s key value:
"abc123"
Command: config authen server_host 10.1.1.222 protocol tacacs+ key "abc123"
Success.
4-22 delete authen serv er_host
Description
This command is used to delete an authentication server host.
Format
delete authen server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
Parameters
tacacs - Specifies the server host’s authentication protocol TACACS.
xtacacs - Specifies the server host’s authentication protocol XTACACS.
tacacs+ - Specifies the server host’s authentication protocol TACACS+.
Restrictions
Only Administrator-level users can issue this command.
Example
To delete an authentication server host:
Command: delete authen server_host 10.1.1.222 protocol tacacs+
Success.
75
Page 81
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show authen server_host
DGS-3620-28PC:admin#
<int 0-255> - Enter the amount of time for user input on console or Telnet. 0 means there is no
time out. The default value is 30 seconds.
4-23 show authen server_hos t
Description
This command is used to display authentication server hosts.
Format
show authen server_host
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To display all authentication server hosts:
Command: show authen server_host
IP Address Protocol Port Timeout Retransmit Key
--------------- -------- ----- ------- ---------- -----------------------
10.1.1.222 TACACS+ 15555 10 ------ 123
Total Entries : 1
4-24 config authen parameter response_timeout
Description
This command is used to configure the amount of time waiting for users to input on the console
and Telnet applications.
Format
config authen parameter response_ti m eout <int 0-255>
Parameters
Restrictions
Only Administrator-level users can issue this command.
76
Page 82
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config authen parameter response_timeout 60
DGS-3620-28PC:admin#
<int 1-255> - Enter the amount of attempts for users trying to login or promote the privilege on
console or Telnet. The default value is 3.
DGS-3620-28PC:admin#config authen parameter attempt 9
DGS-3620-28PC:admin#
Example
To configure 60 seconds for user to input:
Command: config authen parameter response_timeout 60
Success.
4-25 config authen parameter attempt
Description
This command is used to configure the maximum attempts for users trying to login or promote the
privilege on console or Telnet applications. If the failure value is exceeded, connection or access
will be locked.
Format
config authen parameter attempt <int 1-255>
Parameters
Restrictions
Only Administrator-level users can issue this command.
Example
To configure the maximum attempts for users trying to login or promote the privilege to be 9:
Command: config authen parameter attempt 9
Success.
4-26 show authen parameter
Description
This command is used to display the authentication parameters.
Format
show authen parameter
77
Page 83
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin# show authen parameter
DGS-3620-28PC:admin#
DGS-3620-28PC:admin# enable admin
Password:********
Parameters
None.
Restrictions
Only Administrator-level users can issue this command.
Example
To display the authentication parameters:
Command: show authen parameter
Response Timeout : 60 seconds
User Attempts : 9
4-27 enable admin
Description
This command is used to promote the "user" privilege level to "admin" level. When the user enters
this command, the authentication method RADIUS, TACACS, XTACAS, TACACS+, user-defined
server groups, local enable, or none will be used to authenticate the user. Because TACACS,
XTACACS and RADIUS don't support the enable function by themselves, if a user wants to use
either one of these three protocols to enable authentication, the user must create a special
account on the server host first, which has a username enable and then configure its password as
the enable password to support the "enable" function. This command cannot be used when
authentication policy is disabled.
Format
enable admin
Parameters
None.
Restrictions
None.
Example
To enable administrator lever privilege:
78
Page 84
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#
encrypt - (Optional) Specifies the encryption method used.
the password is case-sensitive.
DGS-3620-28PC:admin#config admin local_enable
DGS-3620-28PC:admin#
4-28 config admin local_enabl e
Description
This command is used to configure the local enable password for the enable command. When the
user chooses the local_enable method to promote the privilege level, the enable password of the
local device is needed.
Format
config admin local_enable {encrypt [plain_text | sha_1] <password>}
Parameters
plain_text - Specifies that the password will be in the plain text form.
sha_1 - Specifies that the password will be in the SHA-1 encrypted form.
<password> - Enter the password. Plain text password must be between 0 and 15
characters. The length of SHA-1 encrypted passwords are fixed to 35 bytes long and
Restrictions
Only Administrator-level users can issue this command.
Example
To configure the administrator password:
Command: config admin local_ebable
Enter the old password:
Enter the case-sensitive new password:******
Enter the new password again for confirmation:******
Success.
4-29 create aaa server _group
Description
This command is used to create a group of user-defined AAA servers. The maximum number of
supported server groups, including the built-in server groups, is 8. Each group can have a
maximum of 8 server hosts.
Format
create aaa server_group <string 15>
79
Page 85
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<string 15> - Enter the user-defined server group name.
DGS-3620-28PC:admin#create aaa server_group mix_1
DGS-3620-28PC:admin#
tacacs - Specifies the built-in TACACS server group.
xtacacs - Specifies t he buil t-in XTACACS server group.
tacacs+ - Specifies the built-in TACACS+ server group.
radius - Specifies the built-in RADIUS server group.
group_name - Specifies a user-defined server group.
<string 15> - Enter the name of the server group.
add - Add a server host to the server group.
delete - Remove a server host to the server group.
server_host - Specifies the server host.
radius - Specifies the server host using RADIUS protocol.
Parameters
Restrictions
Only Administrator level can issue this command.
Example
To create a user-defined AAA server group called “mix_1”:
Command: create aaa server_group mix_1
Success.
4-30 config aaa server_group
Description
This command is used to add or remove an AAA server host to or from the specified server group.
The built-in TACACS, XTACACS, TACACS+, and RADIUS server groups only accept server hosts
with the same protocol, but a user-defined server group can accept server hosts with different
protocols.
Format
config aaa server_group [tacacs | xtacacs | tacacs+ | radius | group_name <string 15>] [add
| delete] server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
Parameters
<ipaddr> - Enter the IP address of the server host.
protocol - Specifies the server host protocol.
tacacs - Specifies the server host using TACACS protocol.
xtacacs - Specifies the server host using XTACACS protocol.
tacacs+ - Specifies the server host using TACACS+ protocol.
80
Page 86
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#config aaa server_group group_name mix_1 add server_host
DGS-3620-28PC:admin#
<string 15> - Enter the server group name to be deleted.
DGS-3620-28PC:admin#delete aaa server_group mix_1
DGS-3620-28PC:admin#
Restrictions
Only Administrator level can issue this command.
Example
To To add an AAA server host with an IP address of 10.1.1.222 to server group “mix_1”, specifying
the TACACS+ protocol:
10.1.1.222 protocol tacacs+
Command: config aaa server_group group_name mix_1 add server_host 10.1.1.222
protocol tacacs+
Success.
4-31 delete aaa server_group
Description
This command is used to delete a group of user-defined AAA servers.
Format
delete aaa server_group <string 15 >
Parameters
Restrictions
Only Administrator level can issue this command.
Example
To delete a user-defined AAA server group called “mix_1”:
Command: delete aaa server_group mix_1
Success.
4-32 delete aaa server_host
Description
This command is used to delete an AAA server host.
81
Page 87
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<ipaddr> - Enter the IP address of the server host.
protocol – Specify the protocol.
radius - Specifies RADIUS server host.
DGS-3620-28PC:admin#delete aaa server_host 10.1.1.222 protocol tacacs+
DGS-3620-28PC:admin#
Format
delete aaa server_host <ipaddr> protocol [tacacs | xtacacs | tacacs+ | radius]
Parameters
tacacs – Specify TACACS server host.
xtacacs - Specifies XTACACS server host.
tacacs+ - Specifies TACACS+ server host.
Restrictions
Only Administrator level can issue this command.
Example
To tacacs | xtacacs | tacacs+| delete an AAA server host, with an IP address of 10.1.1.222, that is
running the TACACS+ protocol:
Command: delete aaa server_host 10.1.1.222 protocol tacacs+
Success.
4-33 show aaa
Description
This command is used to display AAA global configuration.
Format
show aaa
Parameters
None.
Restrictions
None.
Example
To display AAA global configuration:
82
Page 88
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show aaa
DGS-3620-28PC:admin#
<string 15> - (Optional) Specifies the built-in or user-defined server group name.
Command: show aaa
Authentication Policy: Enabled
Accounting Network Service State: AAA Method
Accounting Network Service Method: acc_telnet
Accounting Shell Service State: RADIUS Only
Accounting Shell Service Method:
Accounting System Service State: Disabled
Accounting System Service Method:
Accounting Admin Command Service Method:
Accounting Operator Command Service Method:
Accounting PowerUser Command Service Method:
Accounting User Command Service Method:
Authentication Policy Encryption: Enabled
4-34 show aaa server_ group
Description
This command is used to display the groups of AAA servers groups.
Format
show aaa server_group {<string 15>}
Parameters
Restrictions
Only Administrator level can issue this command.
Example
To display all AAA server groups:
83
Page 89
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#show aaa server_group
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show aaa server_host
DGS-3620-28PC:admin#
Command: show aaa server_group
Group Name IP Address Protocol
--------------- --------------------------------------- -------mix_1 --------------------------------------- -------radius --------------------------------------- -------tacacs --------------------------------------- -------tacacs+ --------------------------------------- -------xtacacs --------------------------------------- --------
Total Entries : 5
4-35 show aaa server_ host
Description
This command is used to display the AAA server hosts.
Format
show aaa server_host
Parameters
None.
Restrictions
Only Administrator level can issue this command.
Example
To display all AAA server hosts:
Command: show aaa server_host
IP Address Protocl Port Acct Time Retry Key
Port out
-------------------- ------- ----- ----- ---- ----- ---------------------------
10.1.1.222 RADIUS 15555 1813 10 2 ******
Total Entries : 1
84
Page 90
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#enable aaa_server_password_encryption
DGS-3620-28PC:admin#
4-36 enable aaa_server_password_encryption
Description
This command is used to enable AAA server password encryption.
Format
enable aaa_server_pass word_encryption
Parameters
None.
Restrictions
Only Administrator level can issue this command.
Example
To enable AAA server password encryption:
Command: enable aaa_server_password_encryption
Success.
4-37 disable aaa_server_password_encrypti on
Description
This command is used to disable AAA server password encryption.
Format
disable aaa_server_pass word_encryption
Parameters
None.
Restrictions
Only Administrator level can issue this command.
Example
To disable AAA server password encryption:
85
Page 91
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#disable aaa_server_password_encryption
DGS-3620-28PC:admin#
default - Specifies the default method list of accounting methods.
method_list_name - Specifies the user-defined method list of accounting methods.
characters long.
method - Specifies the accounting method used.
none - Specifies no accounting.
DGS-3620-28PC:admin#config accounting method_list_name shell_acct method
DGS-3620-28PC:admin#
Command: disable aaa_server_password_encryption
Success.
4-38 config accounting
Description
This command is used to configure a user-defined or default method list of accounting methods.
Format
config accounting [default | method_list_name <string 15>] method {tacacs+ | radius |
server_group <string 15> | none}
Parameters
<string 15> - Enter the user-defined method list name here. This name can be up to 15
tacacs+ - Specifies to use the built-in server group 'tacacs+'.
radius - Specifies to use the built-in server group 'radius'.
server_group - Specifies the user-defined server group. If the group contains 'tacacs' or
'xtacacs' server, it will be skipped in accounting.
<string 15> - Enter the user-defined server group name here. This name can be up to 15
characters long.
Restrictions
Only Administrator level users can issue this command.
Example
To configure a user-defined method list called “shell_acct”, that specifies a sequence of the built-in
“tacacs+” server group, followed by the “radius” server group for accounting service on switch:
tacacs+ radius
Command: config accounting method_list_name shell_acct method tacacs+ radius
Success.
86
Page 92
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
network - Specifies that when enabled, the Switch will send informational packets to a remote
Switch. By default, the service is disabled.
shell - Specifies that when enabled, the Switch will send informational packets to a remote
console, Telnet, or SSH. By default, the service is disabled.
system - Specifies that when enabled, the Switch will send informational packets to a remote
boot. By default, the service is disabled.
state - Specifies the state of the accounting service.
disable - Disable the specified accounting service.
DGS-3620-28PC:admin# config accounting service shell state enable
DGS-3620-28PC:admin#
4-39 config accounting service
Description
This command is used to configure the state of the specified RADIUS accounting service.
Format
config accounting service [network | shell | system] state [enable {[radius_only |
method_list_name <string 15> | default_method_list]} | disable]
Parameters
RADIUS server when 802.1X, WAC and JWAC port access control events occur on the
RADIUS server when a user either logs in, logs out or times out on the Switch, using the
RADIUS server when system events occur on the Switch, such as a system reset or system
enable - Enable the specified accounting service.
radius_only - Specifies that the accounting service should only use the RADIUS group
specified by the config radius add <server_index 1-3> [<serv er_i p> | <ipv6addr>]”
command.
method_list_name - Specifies that the accounting service should use the AAA user-
defined method list specified by the “create accounting method_list_name <string 15>”
command.
<string 15> - Enter the method list name used here. This name can be up to 15
characters long.
default_method_list - Specifies that the accounting service should use the AAA default
method list.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the state of the RADIUS accounting service shell to enable:
Command: config accounting service shell state enable
Success
4-40 config accounting service command
Description
This command is used to configure the state of the specified accounting service.
87
Page 93
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
administrator - (Optional) Specifies the accounting service for all administrator level commands.
operator - (Optional) Specifies the accounting service for all operator level commands.
power_user - (Optional) Specifies the accounting service for all power-user level commands.
user - (Optional) Specifies the accounting service for all user level commands.
method_list_name - Specifies the accounting service by the AAA user-defined method list.
none - Specifies to disable accounting services for the specified command level.
DGS-3620-28PC:admin#config accounting service command administrator
DGS-3620-28PC:admin#
<string 15> - Enter the name of the user-defined method list here. This name can be up to 15
characters long.
Format
config accounting service command {a d ministrator | operator | power_user | user}
[method_list_name <string> | no n e]
Parameters
Note: The accounting command only supports the TACACS+ server. The other servers that
exist in the method list will be skipped.
<string> - Enter the method list name used here.
Restrictions
Only Administrators, Operators and Power-Users can issue this command.
Example
To configure the AAA accounting methodlist “admin_acct” for accounting to all a d ministrator
commands:
method_list_name admin_acct
Command: config accounting service command administrator method_list_name
admin_acct
Success.
4-41 create accounting method_list_name
Description
This command is used to create a user-defined method list of accounting methods.
Format
create accounting method_lis t_name <string 15>
Parameters
Restrictions
Only Administrator level users can issue this command.
88
Page 94
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
DGS-3620-28PC:admin#create accounting method_list_name shell_acct
DGS-3620-28PC:admin#
<string 15> - Enter the name of the user-defined method list here. This name can be up to 15
characters long.
DGS-3620-28PC:admin#delete accounting method_list_name shell_acct
DGS-3620-28PC:admin#
Example
To create a user-defined accounting method list called “shell_acct”:
Command: create accounting method_list_name shell_acct
Success.
4-42 delete accounting method_list_name
Description
This command is used to delete a user-defined method list of accounting methods.
Format
delete accounting method_list_ n ame <string 15>
Parameters
Restrictions
Only Administrator level users can issue this command.
Example
To delete the user-defined accounting method list called “shell_acct” from switch:
Command: delete accounting method_list_name shell_acct
Success.
4-43 show accounting
Description
This command is used to display the method list of accounting methods on switch.
Format
show accounting [default | method_list_name <string 15> | all]
89
Page 95
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
default - Displays the user-defined list of default accounting methods.
method_list_name - Displays the user-defined list of specific accounting methods.
all - Displays all accounting method lists on switch.
DGS-3620-28PC:admin#show accounting method_list_name shell_acct
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show accounting service
Network : Disabled
Parameters
<string 15> - Enter the user-defined method list name here. This name can be up to 15
characters long.
Restrictions
Only Administrator level users can issue this command.
Example
To display the user-defined accounting method list called “shell_acct”:
Command: show accounting method_list_name shell_acct
Method List Name Priority Method Name Comment
---------------- -------- --------------- -----------------shell_acct 1 none Keyword
4-44 show accounting service
Description
This command is used to display RADIUS accounting service information.
Format
show accounting service
Parameters
None.
Restrictions
None.
Example
To display accounting service information:
Command: show accounting service
Accounting State
-------------------
90
Page 96
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
Shell : Disabled
DGS-3620-28PC:admin#
<ipaddr> - Enter the IP address of the server host.
auth_port - (Optional) Spe c if ies the port of the RADIUS authentication.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 1812.
acct_port - (Optional) Specifies the port of the RAIDUS accounting.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 1813.
key - (Optional) Specif ies the key for RADIUS.
none - No encryption for RADIUS.
encryption_key - (Optional) The encrypted form key string for RADIUS. The encryption
<key_string 344> - Etner the string with maximum 344 characters.
timeout - (Optional) Specifies the time in second to wait for the server to reply.
<int 1-255> - Enter the value between 1 and 255. The default value is 5.
retransmit - (Optional) Specifies the count for re-transmissions.
<int 1-20> - Enter the value between 1 and 20. The default value is 2.
DGS-3620-28PC:admin#create radius server_host 10.1.1.222 auth_port 15555
DGS-3620-28PC:admin#
System : Disabled
4-45 create radius server_host
Description
This command is used to create an RADIUS server host.
Format
create radius server_host <ipaddr> {auth_port <int 1-65535> | acct_port <int 1-65535> | [key
[<key_string 254> | none] | encryption_key <key_string 344>] | timeout <int 1-255> |
retransmit <int 1-20>}
Parameters
<key_string 254> - Enter the plain text key string for RADIUS.
algorithm is based on DES.
Restrictions
Only Administrator level can issue this command.
Example
To create an RADIUS server host:
timeout 10
Command: create radius server_host 10.1.1.222 auth_port 15555 timeout 10
Key is empty for TACACS+ or RADIUS.
Success.
91
Page 97
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<ipaddr> - Enter the IP address of the server host.
auth_port - (Optional) Spe c if ies the port of the RADIUS authentication.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 1812.
acct_port - (Optional) Specifies the port of the RAIDUS accounting.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 1813.
key - (Optional) Specif ies the key for RADIUS.
none - No encryption for RADIUS.
encryption_key - (Optional) The encrypted form key string for RADIUS. The encryption
<key_string 344> - Etner the string with maximum 344 characters.
timeout - (Optional) Specifies the time in second to wait for the server to reply.
<int 1-255> - Enter the value between 1 and 255. The default value is 5.
retransmit - (Optional) Specifies the count for re-transmissions.
<int 1-20> - Enter the value between 1 and 20. The default value is 2.
DGS-3620-28PC:admin#config radius server_host 10.1.1.222 key "abc123"
DGS-3620-28PC:admin#
4-46 config radius server_host
Description
This command is used to configure the RADIUS server host.
Format
config radius server_host <ipaddr> {auth_port <int 1-65535> | acct_port <int 1-65535> | [key
[<key_string 254> | none] | encryption _key <key_string 344>] | timeout <int 1-255> |
retransmit <int 1-20>}
Parameters
<key_string 254> - Enter the plain text key string for RADIUS.
algorithm is based on DES.
Restrictions
Only Administrator level can issue this command.
Example
To configure the RADIUS server host:
Command: config radius server_host 10.1.1.222 key "abc123"
Success.
4-47 config radius source_ipif
Description
This command is used to specify source interface for all outgo ing RAD IUS pac k et s.
Format
config radius source_ipif [<ipif_name 12> {<ipaddr> | <ipv6addr>} | none]
92
Page 98
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<ipif_name 12> - Enter the IP interface name used here.
<ipaddr> - Enter the IPv4 address used here.
<ipv6addr> - Enter the IPv6 address used here.
none - Specifies to revert to the default route table for all outgoing RADIUS packet.
DGS-3620-28PC:admin#config radius source_ipif if_v200
DGS-3620-28PC:admin#
DGS-3620-28PC:admin#show radius source_ipif
DGS-3620-28PC:admin#
Parameters
Restrictions
Only Administrator level can issue this command.
Example
To specify an interface as the source interface for all outgoing RADIUS packets.
Command: config radius source_ipif if_v200
Success.
4-48 show radius source_ipif
Description
This command is used to display specified source interface for all outgoing RADIUS packets.
Format
show radius source_ipif
Parameters
None.
Restrictions
Only Administrator level can issue this command.
Example
To display specified source interface for all outgoing RADIUS packets.
Command: show radius source_ipif
IP Interface : if_v200
IPv4 Address : None
IPv6 Address : None
93
Page 99
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
<ipaddr> - Enter the IP address of the server host.
port - (Optional) The port number of the TACACS server host.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 49.
timeout - (Optional) Specifies the time in second to wait for the server to reply.
<int 1-255> - Enter the value between 1 and 255. The default value is 5.
retransmit - (Optional) Specifies the count for re-transmissions.
<int 1-20> - Enter the value between 1 and 20. The default value is 2.
DGS-3620-28PC:admin#create tacacs server_host 10.1.1.223 port 15555 timeout 10
DGS-3620-28PC:admin#
<ipaddr> - Enter the IP address of the server host.
port - (Optional) The port number of the TACACS server host.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 49.
4-49 create tacacs server_host
Description
This command is used to create a TACACS server host.
Format
create tacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit
<int 1-20>}
Parameters
Restrictions
Only Administrator level can issue this command.
Example
To create a TACACS server host:
Command: create tacacs server_host 10.1.1.223 port 15555 timeout 10
Success.
4-50 config tacacs server_host
Description
This command is used to configure a TACACS server host.
Format
config tacacs server_host <ipaddr> {port <int 1-65535> | timeout <int 1-255> | retransmit
<int 1-20>}
Parameters
94
Page 100
xStack® DGS-3620 Series Layer 3 Managed Stackable Gigabit Switch CLI Reference Guide
timeout - (Optional) Specifies the time in second to wait for the server to reply.
<int 1-255> - Enter the value between 1 and 255. The default value is 5.
retransmit - (Optional) Specifies the count for re-transmissions.
<int 1-20> - Enter the value between 1 and 20. The default value is 2.
DGS-3620-28PC:admin#config tacacs server_host 10.1.1.223 retransmit 5
DGS-3620-28PC:admin#
<ipaddr> - Enter the IP address of the server host.
port - (Optional) The port number of the TACACS+ server host.
<int 1-65535> - Enter the value between 1 and 65535. The default value is 49.
key - (Optional) Specif ies the key for TACACS+.
none - No encryption for RADIUS.
encryption_key - (Optional) The encrypted form key string for TACACS+. The encryption
<key_string 344> - Etner the string with maximum 344 characters.
timeout - (Optional) Specifies the time in second to wait for the server to reply.
<int 1-255> - Enter the value between 1 and 255. The default value is 5.
Restrictions
Only Administrator level can issue this command.
Example
To configure the TACACS server host:
Command: config tacacs server_host 10.1.1.223 retransmit 5
Key is meaningless for TACACS and XTACACS.
Success.
4-51 create tacacs+ server_host
Description
This command is used to create a TACACS+ server host.
Format
create tacacs+ server_host <ipaddr> {port <int 1-65535> | [key [<key_string 254> | none] |
encryption_key <key_string 344>] | timeout <int 1-255>}
Parameters
<key_string 254> - Enter the plain text key string for TACACS+.
algorithm is based on DES.
Restrictions
Only Administrator level can issue this command.
Example
To create a TACACS+ server host:
95
 Loading...