

Page 1
CLI Reference Guide
DES-1210-28/ME
Metro Ethernet Managed Switch
V1.1
Page 2
Information in this document is subject to change without notice.
© 2009 D-Link Computer Corporation. All rights reserved.
Reproduction in any manner whatsoever without the written permission of D-Link Computer Corporation
is strictly forbidden.
Trademarks used in this text: D-Link and the D-Link logo are trademarks of D-Link Computer
Corporation; Microsoft and Windows are registered trademarks of Microsoft Corporation.
Other trademarks and trade names may be used in this document to refer to either the entities claiming
the marks and names or their products. D-Link Computer Corporation disclaims any proprietary interest
in trademarks and trade names other than its own.
FCC Warning
This equipment has been tested and found to comply with the limits for a Class A digital device,
pursuant to Part 15 of the FCC Rules. These limits are designed to provide reasonable protection against
harmful interference when the equipment is operated in a commercial environment. This equipment
generates, uses, and can radiate radio frequency energy and, if not installed and used in accordance
with this user’s guide, may cause harmful interference to radio communications. Operation of this
equipment in a residential area is likely to cause harmful interference in which case the user will be
required to correct the interference at hisown expense.
CE Mark Warning
This is a Class A product. In a domestic environment, this product may cause radio interference in
which case the user may be required to take adequate measures.
Warnung!
Dies ist ein Produkt der Klasse A. Im Wohnbereich kann dieses Produkt Funkstoerungen verursachen. In
diesem Fall kann vom Benutzer verlangt werden, angemessene Massnahmen zu ergreifen.
Precaución!
Este es un producto de Clase A. En un entorno doméstico, puede causar interferencias de radio, en
cuyo case, puede requerirse al usuario para que adopte las medidas adecuadas.
Attention!
Ceci est un produit de classe A. Dans un environnement domestique, ce produit pourrait causer des
interférences radio, auquel cas l`utilisateur devrait prendre les mesures adéquates.
Attenzione!
Il presente prodotto appartiene alla classe A. Se utilizzato in ambiente domestico il prodotto può causare
interferenze radio, nel cui caso è possibile che l`utente debba assumere provvedimenti adeguati.
VCCI Warning
January, 2012
Page 3
Table of Contents
INTRODUCTION...................................................................................................................................................... 1
USING THE CONSOLE CLI.................................................................................................................................... 3
COMMAND SYNTAX .............................................................................................................................................. 7
BASIC SWITCH COMMANDS .............................................................................................................................. 10
enable password encryption................................................................................................................................................. 10
disable password encryption................................................................................................................................................ 11
create account ...................................................................................................................................................................... 11
config account ..................................................................................................................................................................... 12
show account ....................................................................................................................................................................... 13
delete account ...................................................................................................................................................................... 13
show session ........................................................................................................................................................................ 14
show switch ......................................................................................................................................................................... 14
enable web ........................................................................................................................................................................... 15
disable web .......................................................................................................................................................................... 16
enable autoconfig ................................................................................................................................................................ 16
disable autoconfig................................................................................................................................................................ 17
show autoconfig .................................................................................................................................................................. 17
save...................................................................................................................................................................................... 17
reboot................................................................................................................................................................................... 18
reset ..................................................................................................................................................................................... 19
logout................................................................................................................................................................................... 19
ping...................................................................................................................................................................................... 20
enable telnet......................................................................................................................................................................... 20
disable telnet........................................................................................................................................................................ 21
show tech support ................................................................................................................................................................ 21
SMTP SERVER COMMANDS............................................................................................................................... 23
enable smtp.......................................................................................................................................................................... 23
disable smtp ......................................................................................................................................................................... 23
config smtp .......................................................................................................................................................................... 24
show smtp............................................................................................................................................................................ 24
smtp sent_testmsg................................................................................................................................................................ 25
MODIFY BANNER AND PROMPT COMMANDS................................................................................................. 26
config command_prompt..................................................................................................................................................... 26
config greeting_message ..................................................................................................................................................... 27
show greeting_message ....................................................................................................................................................... 28
SWITCH PORT COMMANDS ............................................................................................................................... 29
config ports.......................................................................................................................................................................... 29
show ports............................................................................................................................................................................ 30
LOOPBACK DETECTION COMMANDS .............................................................................................................. 31
config loopdetect ................................................................................................................................................................. 31
config loopdetect mode ....................................................................................................................................................... 31
config loopdetect ports ........................................................................................................................................................ 32
config loopdetect ................................................................................................................................................................. 32
show loopdetect ................................................................................................................................................................... 33
DOS PREVENTION COMMANDS ........................................................................................................................ 34
Page 4
config dos_prevention dos_type.......................................................................................................................................... 34
show dos_prevention ........................................................................................................................................................... 35
clear dos_prevention counters ............................................................................................................................................. 36
enable dos_prevention trap_log........................................................................................................................................... 36
disable dos_prevention trap_log.......................................................................................................................................... 37
PPPOE CIRCUIT ID INSERTION COMMANDS ................................................................................................... 38
config pppoe circuit_id_insertion state................................................................................................................................ 38
config pppoe circuit_id_insertion ports ............................................................................................................................... 39
show pppoe circuit_id_insertion.......................................................................................................................................... 39
show pppoe circuit_id_insertion ports................................................................................................................................. 40
DHCP SERVER SCREENING COMMANDS........................................................................................................ 41
config filter dhcp_server...................................................................................................................................................... 41
show filter dhcp_server ....................................................................................................................................................... 42
config dhcp_server screening ports ..................................................................................................................................... 43
show dhcp_server screening................................................................................................................................................ 43
IP-MAC-PORT BINDING COMMANDS ................................................................................................................ 45
create address_binding ip_mac ipaddress............................................................................................................................ 45
config address_binding ip_mac ports .................................................................................................................................. 46
config address_binding auto_scan....................................................................................................................................... 46
delete address_binding ........................................................................................................................................................ 47
show address_binding ......................................................................................................................................................... 48
show address_binding auto_scan list................................................................................................................................... 49
enable address_binding dhcp_snoop ................................................................................................................................... 49
disable address_binding dhcp_snoop .................................................................................................................................. 49
NETWORK MANAGEMENT (SNMP) COMMANDS............................................................................................. 51
create snmp user .................................................................................................................................................................. 53
delete snmp user .................................................................................................................................................................. 54
show snmp user ................................................................................................................................................................... 54
create snmp view ................................................................................................................................................................. 55
delete snmp view ................................................................................................................................................................. 56
show snmp view .................................................................................................................................................................. 56
create snmp community....................................................................................................................................................... 57
delete snmp community....................................................................................................................................................... 57
show snmp community ........................................................................................................................................................ 58
config snmp engineID ......................................................................................................................................................... 58
show snmp engineID ........................................................................................................................................................... 59
create snmp group ............................................................................................................................................................... 59
delete snmp group ............................................................................................................................................................... 61
show snmp global state........................................................................................................................................................ 61
show snmp groups ............................................................................................................................................................... 61
create snmp host .................................................................................................................................................................. 62
delete snmp host .................................................................................................................................................................. 63
show snmp host ................................................................................................................................................................... 64
enable trusted_host .............................................................................................................................................................. 64
disable trusted_host ............................................................................................................................................................. 65
create trusted_host ............................................................................................................................................................... 65
show trusted_host ................................................................................................................................................................ 65
Page 5
delete trusted_host ............................................................................................................................................................... 66
enable snmp traps ................................................................................................................................................................ 67
disable snmp traps ............................................................................................................................................................... 67
enable snmp authenticate trap.............................................................................................................................................. 67
disable snmp authenticate trap............................................................................................................................................. 68
show snmp traps .................................................................................................................................................................. 68
config syslocation ................................................................................................................................................................ 69
config sysname .................................................................................................................................................................... 69
enable snmp ......................................................................................................................................................................... 69
disable snmp ........................................................................................................................................................................ 70
enable snmp DHCP_ screening traps .................................................................................................................................. 70
disable snmp DHCP_ screening traps ................................................................................................................................. 71
enable snmp IMPB_violation traps ..................................................................................................................................... 71
disable snmp IMPB_violation traps .................................................................................................................................... 71
enable snmp fiber_port_link traps ....................................................................................................................................... 72
disable snmp fiber_port_link traps ...................................................................................................................................... 72
enable snmp firmware_upgrade_state traps......................................................................................................................... 73
disable snmp firmware_upgrade_state traps........................................................................................................................ 73
enable snmp LBD traps ....................................................................................................................................................... 73
disable snmp LBD traps ...................................................................................................................................................... 74
enable snmp port_security_violation traps .......................................................................................................................... 74
disable snmp port_security_violation traps ......................................................................................................................... 75
enable snmp rstpport_state_change traps ............................................................................................................................ 75
disable snmp rstpport_state_change traps ........................................................................................................................... 76
enable snmp system_device_bootup traps ........................................................................................................................... 76
disable snmp system_device_bootup traps .......................................................................................................................... 76
enable snmp twistedpair_port_link traps ............................................................................................................................. 77
disable snmp twistedpair_port_link traps ............................................................................................................................ 77
enable snmp duplicate_IP_detected traps ............................................................................................................................ 78
disable snmp duplicate_IP_detected traps ........................................................................................................................... 78
DOWNLOAD/UPLOAD COMMANDS................................................................................................................... 79
download ............................................................................................................................................................................. 79
upload .................................................................................................................................................................................. 80
DHCP RELAY COMMANDS ................................................................................................................................. 82
enable dhcp_relay ................................................................................................................................................................ 82
disable dhcp_relay ............................................................................................................................................................... 83
config dhcp_relay add ipif system....................................................................................................................................... 83
config dhcp_relay delete ipif system ................................................................................................................................... 84
config dhcp_relay ................................................................................................................................................................ 84
config dhcp_relay option_82 ............................................................................................................................................... 85
show dhcp_relay .................................................................................................................................................................. 86
enable dhcp_local_relay ...................................................................................................................................................... 86
disable dhcp_local_relay ..................................................................................................................................................... 87
config dhcp_local_relay vlan............................................................................................................................................... 87
show dhcp_local_relay ........................................................................................................................................................ 88
GRATUITOUS ARP COMMANDS ........................................................................................................................ 89
config gratuitous_arp send ipif_status_up ........................................................................................................................... 89
Page 6
config gratuitous_arp send dup_ip_detected ....................................................................................................................... 90
config gratuitous_arp learning............................................................................................................................................. 90
enable gratuitous_arp........................................................................................................................................................... 91
disable gratuitous_arp.......................................................................................................................................................... 91
show gratuitous_arp............................................................................................................................................................. 92
config gratuitous_arp send periodically interval ................................................................................................................. 92
NETWORK MONITORING COMMANDS ............................................................................................................. 94
show packet ports ................................................................................................................................................................ 94
show error ports ................................................................................................................................................................... 95
show utilization ................................................................................................................................................................... 96
clear counters....................................................................................................................................................................... 97
clear log ............................................................................................................................................................................... 97
show log .............................................................................................................................................................................. 97
enable syslog ....................................................................................................................................................................... 98
disable syslog ...................................................................................................................................................................... 98
show syslog ......................................................................................................................................................................... 99
create syslog host................................................................................................................................................................. 99
config syslog host .............................................................................................................................................................. 101
delete syslog host............................................................................................................................................................... 103
show syslog host................................................................................................................................................................ 104
cable diagnostic port .......................................................................................................................................................... 104
SPANNING TREE COMMANDS......................................................................................................................... 106
config stp ........................................................................................................................................................................... 106
config stp ports .................................................................................................................................................................. 107
config stp version .............................................................................................................................................................. 109
config stp fbpdu ................................................................................................................................................................. 109
config stp priority .............................................................................................................................................................. 110
enable stp........................................................................................................................................................................... 110
disable stp .......................................................................................................................................................................... 110
show stp............................................................................................................................................................................. 111
show stp ports .................................................................................................................................................................... 112
show stp instance ............................................................................................................................................................... 113
show stp mst_config_id ..................................................................................................................................................... 114
create stp instance_id......................................................................................................................................................... 114
delete stp instance_id......................................................................................................................................................... 115
config stp mst_config_id ................................................................................................................................................... 115
config stp mst_ports .......................................................................................................................................................... 116
FORWARDING DATABASE COMMANDS ........................................................................................................ 117
create fdb ........................................................................................................................................................................... 117
create multicast_fdb........................................................................................................................................................... 118
config multicast_fdb .......................................................................................................................................................... 118
config fdb aging_time........................................................................................................................................................ 119
delete fdb ........................................................................................................................................................................... 119
enable flood_fdb ................................................................................................................................................................ 120
disable flood_fdb ............................................................................................................................................................... 120
show flood_fdb.................................................................................................................................................................. 121
clear flood_fdb .................................................................................................................................................................. 121
Page 7
show multicast_fdb............................................................................................................................................................ 121
show fdb ............................................................................................................................................................................ 122
config multicast filter ........................................................................................................................................................ 123
show multicast filter port_mode ........................................................................................................................................ 123
create auto_fdb .................................................................................................................................................................. 124
delete auto_fdb .................................................................................................................................................................. 124
BROADCAST STORM CONTROL COMMANDS .............................................................................................. 126
config traffic control .......................................................................................................................................................... 126
show traffic control............................................................................................................................................................ 127
config traffic trap ............................................................................................................................................................... 127
QOS COMMANDS............................................................................................................................................... 129
config scheduling .............................................................................................................................................................. 130
show scheduling ................................................................................................................................................................ 131
config bandwidth_control.................................................................................................................................................. 132
show bandwidth_control ................................................................................................................................................... 132
config cos mac_mapping ................................................................................................................................................... 133
show cos mac_mapping..................................................................................................................................................... 134
delete cos mac_mapping.................................................................................................................................................... 134
config cos ip_mapping ...................................................................................................................................................... 134
show cos ip_mapping ........................................................................................................................................................ 135
delete cos ip_mapping ....................................................................................................................................................... 135
config cos mapping............................................................................................................................................................ 136
show cos mapping ............................................................................................................................................................. 136
config cos protocol_mapping ............................................................................................................................................ 137
show cos protocol_mapping .............................................................................................................................................. 137
delete cos protocol_mapping ............................................................................................................................................. 138
config cos vlanid_mapping................................................................................................................................................ 138
show cos vlanid_mapping ................................................................................................................................................. 139
delete cos vlanid_mapping ................................................................................................................................................ 139
config cos tos..................................................................................................................................................................... 140
show cos tos....................................................................................................................................................................... 140
config cos tcp_port_mapping ............................................................................................................................................ 141
show cos tcp_port_mapping .............................................................................................................................................. 141
delete cos tcp_port_mapping ............................................................................................................................................. 142
config cos udp_port_mapping ........................................................................................................................................... 142
show cos udp _port_mapping ............................................................................................................................................ 142
delete cos udp_port_mapping............................................................................................................................................ 143
config 802.1p user_priority ............................................................................................................................................... 143
show 802.1p user_priority ................................................................................................................................................. 144
config 802.1p default_priority........................................................................................................................................... 145
show 802.1p default_priority............................................................................................................................................. 145
config scheduling_mechanism .......................................................................................................................................... 146
show scheduling_mechanism ............................................................................................................................................ 147
config dscp mode............................................................................................................................................................... 147
config dscp_mapping......................................................................................................................................................... 147
show dscp_mapping .......................................................................................................................................................... 148
RMON COMMANDS............................................................................................................................................ 149
Page 8
enable rmon ....................................................................................................................................................................... 149
disable rmon ...................................................................................................................................................................... 150
create rmon alarm .............................................................................................................................................................. 150
delete rmon alarm .............................................................................................................................................................. 151
create rmon collection stats ............................................................................................................................................... 151
delete rmon collection stats ............................................................................................................................................... 152
create rmon collection history ........................................................................................................................................... 152
delete rmon collection history ........................................................................................................................................... 153
create rmon event .............................................................................................................................................................. 153
delete rmon event .............................................................................................................................................................. 154
show rmon ......................................................................................................................................................................... 154
PORT MIRRORING COMMANDS ...................................................................................................................... 156
enable mirror ..................................................................................................................................................................... 156
disable mirror .................................................................................................................................................................... 156
config mirror target............................................................................................................................................................ 157
show mirror ....................................................................................................................................................................... 158
VLAN COMMANDS............................................................................................................................................. 159
create vlan.......................................................................................................................................................................... 160
delete vlan.......................................................................................................................................................................... 160
config vlan ......................................................................................................................................................................... 160
config gvrp ........................................................................................................................................................................ 161
config pvid......................................................................................................................................................................... 162
config gvrp timer ............................................................................................................................................................... 162
enable gvrp ........................................................................................................................................................................ 163
disable gvrp ....................................................................................................................................................................... 163
show vlan........................................................................................................................................................................... 164
show gvrp .......................................................................................................................................................................... 164
show gvrp timer ................................................................................................................................................................. 165
enable vlan_trunk .............................................................................................................................................................. 165
disable vlan_trunk ............................................................................................................................................................. 166
show vlan_trunk ................................................................................................................................................................ 166
config vlan_trunk ports...................................................................................................................................................... 167
enable asymmetric_vlan .................................................................................................................................................... 167
disable asymmetric_vlan ................................................................................................................................................... 167
show asymmetric_vlan ...................................................................................................................................................... 168
enable management vlan ................................................................................................................................................... 168
disable management vlan .................................................................................................................................................. 168
config management vlan.................................................................................................................................................... 169
show management vlan ..................................................................................................................................................... 169
Q-IN-Q COMMANDS........................................................................................................................................... 171
enable qinq ........................................................................................................................................................................ 171
disable qinq........................................................................................................................................................................ 172
show qinq .......................................................................................................................................................................... 172
config qinq ports................................................................................................................................................................ 173
create vlan_translation ....................................................................................................................................................... 173
show vlan_translation ........................................................................................................................................................ 174
delete vlan_translation cvid ............................................................................................................................................... 174
Page 9
LINK AGGREGATION COMMANDS.................................................................................................................. 176
create link_aggregation ..................................................................................................................................................... 176
delete link_aggregation ..................................................................................................................................................... 177
config link_aggregation ..................................................................................................................................................... 177
show link_aggregation....................................................................................................................................................... 178
BASIC IP COMMANDS....................................................................................................................................... 179
config ipif System ............................................................................................................................................................. 179
show ipif ............................................................................................................................................................................ 180
BPDU ATTACK PROTECTION COMMANDS.................................................................................................... 181
config bpdu_protection ports............................................................................................................................................. 181
config bpdu_protection recovery_timer ............................................................................................................................ 182
config bpdu_protection...................................................................................................................................................... 183
enable bpdu_protection ..................................................................................................................................................... 183
disable bpdu_protection..................................................................................................................................................... 184
show bpdu_protection ....................................................................................................................................................... 184
MAC NOTIFICATION COMMANDS.................................................................................................................... 186
enable mac_notification..................................................................................................................................................... 186
disable mac_notification .................................................................................................................................................... 186
config mac_notification ..................................................................................................................................................... 187
config mac_notification ports............................................................................................................................................ 187
show mac_notification....................................................................................................................................................... 188
show mac_notification ports.............................................................................................................................................. 188
IGMP SNOOPING COMMANDS......................................................................................................................... 190
config igmp_snooping ....................................................................................................................................................... 191
config igmp_snooping querier........................................................................................................................................... 192
config igmp_snooping querier_selection........................................................................................................................... 192
config igmp_snooping querier_interval............................................................................................................................. 193
config igmp_snooping robustness_variable ...................................................................................................................... 193
create igmp_snooping multicast_vlan ............................................................................................................................... 194
config igmp_snooping multicast_vlan............................................................................................................................... 194
delete igmp_snooping multicast_vlan ............................................................................................................................... 195
config igmp_snooping multicast_vlan_group ................................................................................................................... 195
config igmp_snooping data_driven_learning .................................................................................................................... 196
config igmp_snooping data_driven_learning .................................................................................................................... 196
clear igmp_snooping data_driven_group .......................................................................................................................... 197
config igmp_snooping max_response_time ...................................................................................................................... 197
config router_ports ............................................................................................................................................................ 198
config router_ports_forbidden........................................................................................................................................... 198
config igmp access_authentication ports ........................................................................................................................... 199
show igmp access_authentication ports............................................................................................................................. 199
enable igmp_snooping ....................................................................................................................................................... 200
disable igmp_snooping ...................................................................................................................................................... 200
show igmp_snooping ......................................................................................................................................................... 201
show igmp_snooping group .............................................................................................................................................. 202
show igmp_snooping forwarding ...................................................................................................................................... 202
show igmp_snooping host ................................................................................................................................................. 203
show router_port................................................................................................................................................................ 203
Page 10
LIMITED IP MULTICAST ADDRESS COMMANDS ........................................................................................... 205
create mcast_filter_profile................................................................................................................................................. 205
config mcast_filter_profile profile_id............................................................................................................................... 206
config mcast_filter_profile profile_name ......................................................................................................................... 206
delete mcast_filter_profile................................................................................................................................................. 207
show mcast_filter_profile.................................................................................................................................................. 207
config limited_multicast_addr ports .................................................................................................................................. 208
show limited_multicast_addr............................................................................................................................................. 208
config max_mcast_group ports ......................................................................................................................................... 209
show max_mcast_group ports ........................................................................................................................................... 209
802.1X COMMANDS ........................................................................................................................................... 211
enable 802.1x..................................................................................................................................................................... 212
disable 802.1x.................................................................................................................................................................... 212
show 802.1x....................................................................................................................................................................... 213
config 802.1x feap ............................................................................................................................................................. 213
show 802.1x auth_state ..................................................................................................................................................... 213
show 802.1x feap status..................................................................................................................................................... 214
show 802.1x auth_configuration ....................................................................................................................................... 215
config 802.1x auth_parameter ports .................................................................................................................................. 216
config 802.1x init .............................................................................................................................................................. 217
config 802.1x auth_protocol.............................................................................................................................................. 218
config 802.1x reauth .......................................................................................................................................................... 218
config radius add ............................................................................................................................................................... 218
config radius delete............................................................................................................................................................ 219
config radius ...................................................................................................................................................................... 219
show radius........................................................................................................................................................................ 220
config 802.1x auth_mode .................................................................................................................................................. 221
create 802.1x guest_vlan ................................................................................................................................................... 221
delete 802.1x guest_vlan ................................................................................................................................................... 222
config 802.1x guest_vlan ports.......................................................................................................................................... 222
show 802.1x guest_vlan .................................................................................................................................................... 223
create 802.1x user .............................................................................................................................................................. 223
show 802.1x user ............................................................................................................................................................... 224
delete 802.1x user .............................................................................................................................................................. 224
config 802.1x capability ports ........................................................................................................................................... 225
PORT SECURITY COMMANDS ......................................................................................................................... 226
config port_security ........................................................................................................................................................... 226
show port_security ............................................................................................................................................................ 227
TIME AND SNTP COMMANDS .......................................................................................................................... 228
config sntp ......................................................................................................................................................................... 228
show sntp........................................................................................................................................................................... 229
enable sntp ......................................................................................................................................................................... 229
disable sntp ........................................................................................................................................................................ 230
config time......................................................................................................................................................................... 230
config time_zone operator................................................................................................................................................. 231
config dst ........................................................................................................................................................................... 231
show time .......................................................................................................................................................................... 232
Page 11

ARP COMMANDS ............................................................................................................................................... 234
create ArpSpoofing............................................................................................................................................................ 234
show ArpSpoofing............................................................................................................................................................. 235
delete ArpSpoofing............................................................................................................................................................ 235
config arp_aging time ........................................................................................................................................................ 236
clear arptable ..................................................................................................................................................................... 236
show arpentry .................................................................................................................................................................... 237
show arpentry aging_time ................................................................................................................................................. 237
BANNER COMMANDS ....................................................................................................................................... 238
config log_save_timing ..................................................................................................................................................... 238
show log_save_timing ....................................................................................................................................................... 239
show log ............................................................................................................................................................................ 239
COMMAND HISTORY LIST COMMANDS ......................................................................................................... 240
? ......................................................................................................................................................................................... 240
show command_history..................................................................................................................................................... 241
dir ...................................................................................................................................................................................... 242
SSH COMMANDS ............................................................................................................................................... 243
enable ssh .......................................................................................................................................................................... 243
disable ssh.......................................................................................................................................................................... 244
config ssh algorithm .......................................................................................................................................................... 244
config ssh authmode .......................................................................................................................................................... 245
show ssh authmode............................................................................................................................................................ 245
config ssh server ................................................................................................................................................................ 246
show ssh server.................................................................................................................................................................. 246
show ssh algorithm ............................................................................................................................................................ 247
config ssh user ................................................................................................................................................................... 248
show ssh user authmode .................................................................................................................................................... 248
SSL COMMANDS................................................................................................................................................ 249
enable ssl ........................................................................................................................................................................... 249
disable ssl .......................................................................................................................................................................... 249
show ssl ............................................................................................................................................................................. 250
download ssl certificate ..................................................................................................................................................... 250
ACCESS AUTHENTICATION CONTROL COMMANDS ................................................................................... 252
create authen_login method_list_name ............................................................................................................................. 253
config authen_login ........................................................................................................................................................... 253
delete authen_login method_list_name ............................................................................................................................. 255
show authen_login............................................................................................................................................................. 255
show authen_policy ........................................................................................................................................................... 256
create authen_enable method_list_name ........................................................................................................................... 256
config authen_enable ......................................................................................................................................................... 257
delete authen_enable method_list_name ........................................................................................................................... 258
show authen_enable........................................................................................................................................................... 259
enable authen_policy ......................................................................................................................................................... 259
disable authen_policy ........................................................................................................................................................ 260
config authen application .................................................................................................................................................. 260
show authen application .................................................................................................................................................... 261
config authen parameter .................................................................................................................................................... 262
Page 12
show authen parameter ...................................................................................................................................................... 262
create authen server_host .................................................................................................................................................. 263
config authen server_host .................................................................................................................................................. 264
delete authen server_host .................................................................................................................................................. 265
show authen server_host.................................................................................................................................................... 265
create authen server_group................................................................................................................................................ 266
config authen server_group ............................................................................................................................................... 267
delete authen server_group................................................................................................................................................ 268
show authen server_host.................................................................................................................................................... 268
enable admin...................................................................................................................................................................... 269
config admin local_enable ................................................................................................................................................. 269
LACP COMMANDS............................................................................................................................................. 271
config lacp port_priority.................................................................................................................................................... 271
show lacp........................................................................................................................................................................... 271
LLDP COMMANDS ............................................................................................................................................. 273
enable lldp ......................................................................................................................................................................... 273
disable lldp ........................................................................................................................................................................ 274
config lldp message_tx_interval........................................................................................................................................ 274
config lldp message_tx_hold_multiplier ........................................................................................................................... 275
config lldp reinit_delay...................................................................................................................................................... 275
config lldp tx_delay ........................................................................................................................................................... 276
show lldp ........................................................................................................................................................................... 276
show lldp ports .................................................................................................................................................................. 277
show lldp local_ports......................................................................................................................................................... 278
show lldp remote_ports ..................................................................................................................................................... 279
config lldp ports................................................................................................................................................................. 279
show lldp mgt_addr ........................................................................................................................................................... 283
show lldp statistics............................................................................................................................................................. 283
ACCESS CONTROL LIST COMMANDS............................................................................................................ 285
create access_profile.......................................................................................................................................................... 286
config access_profile ......................................................................................................................................................... 287
delete access_profile.......................................................................................................................................................... 290
show access_profile ........................................................................................................................................................... 290
create cpu_access_profile.................................................................................................................................................. 291
config cpu_access_profile ................................................................................................................................................. 292
delete cpu_access_profile.................................................................................................................................................. 294
show cpu_access_profile ................................................................................................................................................... 295
TRAFFIC SEGMENTATION COMMANDS ......................................................................................................... 296
config traffic_segmentation ............................................................................................................................................... 296
show traffic_segmentation................................................................................................................................................. 296
SAFEGUARD COMMANDS................................................................................................................................ 298
config safeguard_engine .................................................................................................................................................... 298
show safeguard_engine ..................................................................................................................................................... 298
DEVICE SPECIFICATIONS ................................................................................................................................ 300
Technical Specifications .................................................................................................................................................... 300
Cable Lengths.................................................................................................................................................................... 302
Page 13
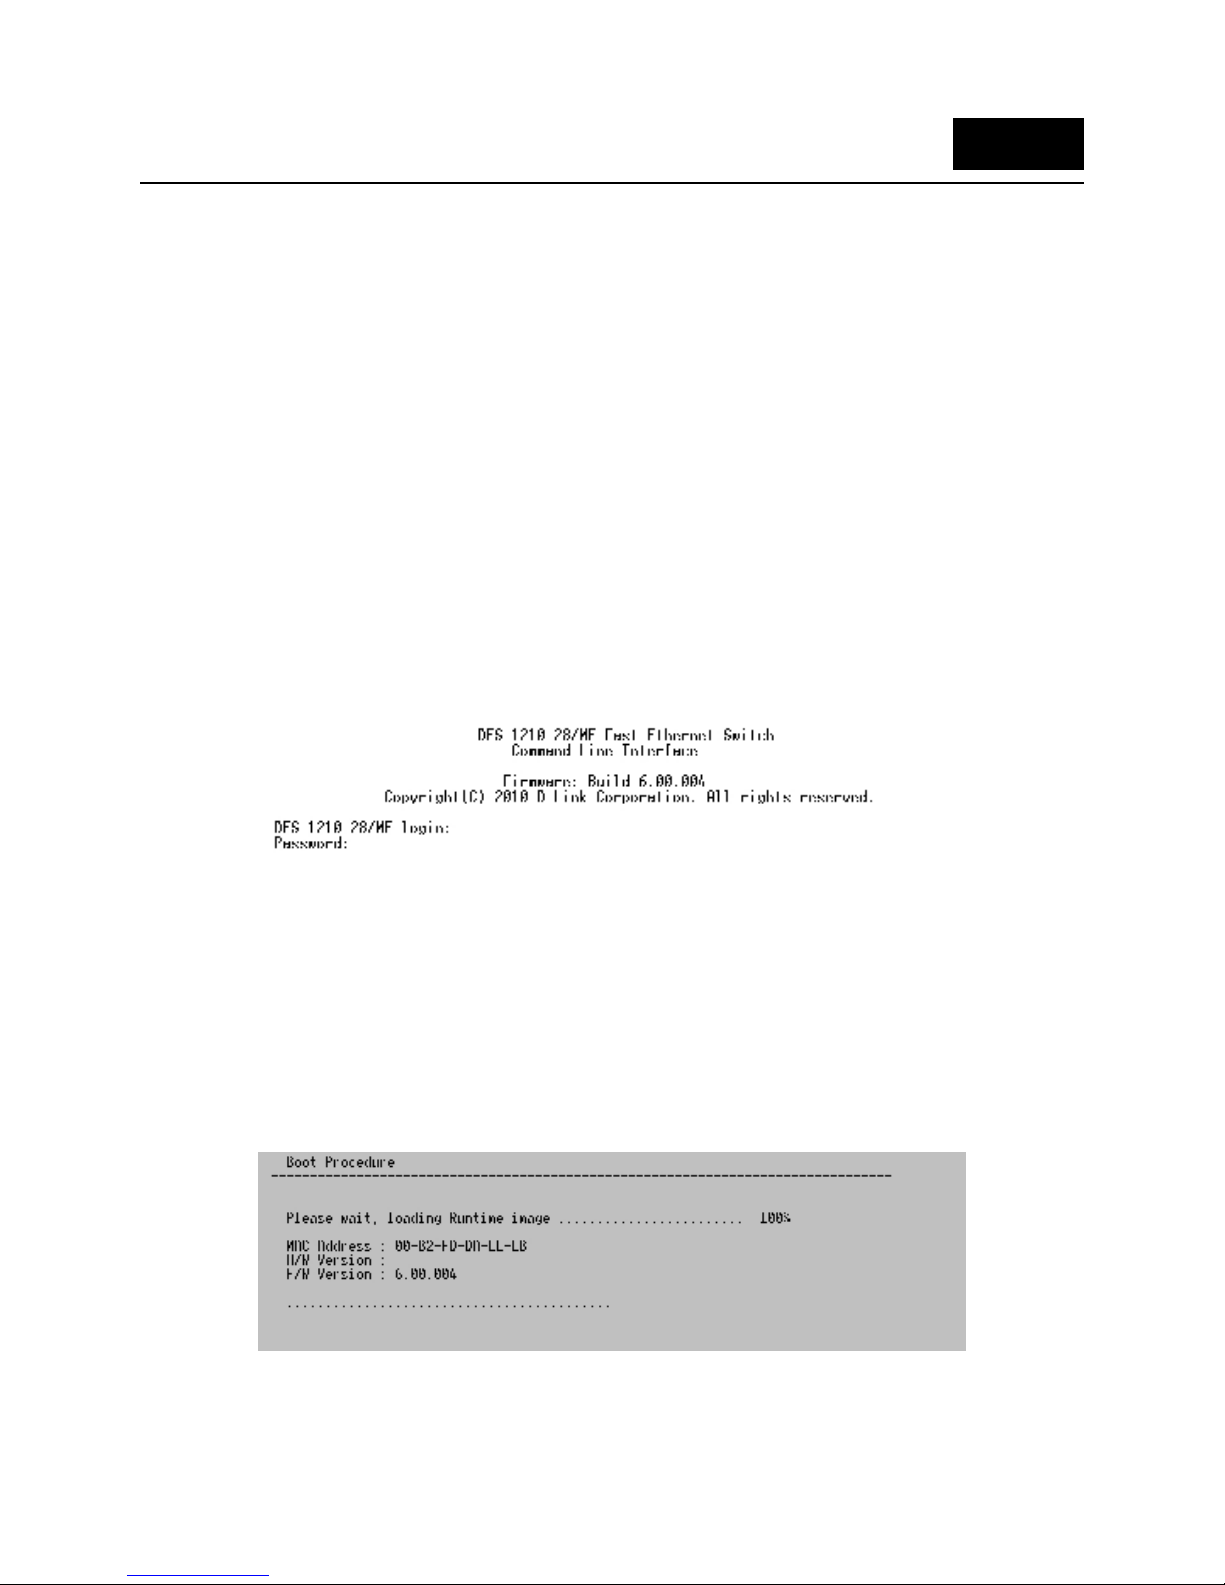
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
1
1
11
1
INTRODUCTION
The DES-1210-28/ME consists of 24 10/100Mbps ports plus 2 combo 10/100/100/SFP ports and 2
dedicated SFP ports.
The Switch can be managed through the Switch’s serial port, Telnet, or the Web-based management
agent. The Command Line Interface (CLI) can be used to configure and manage the Switch via the serial
port or Telnet interfaces.
This manual provides a reference for all of the commands contained in the CLI. Configuration and
management of the Switch via the Web-based management agent is discussed in the Manual. For
detailed information on installing hardware please refer also to the Manual.
Accessing the Switch via the Serial Port
The Switch’s serial port’s default settings are as follows:
• 9600 bps
• No parity
• 8 data bits
• 1 stop bit
A computer running a terminal emulation program capable of emulating a VT-100 terminal and a serial
port configured as above then connected to the Switch’s serial port via an RJ-45 cable.
With the serial port properly connected to a management computer, the following screen should be
visible. If this screen does not appear, try pressing Ctrl+r to refresh the console screen.
Figure 1–1 Initial CLI screen
There is no initial username or password. Just press the Enter key twice to display the CLI input cursor
− DES-1210-28/ME:5#. This is the command line where all commands are input.
Setting the Switch’s IP Address
Each Switch must be assigned its own IP Address, which is used for communication with an SNMP
network manager or other TCP/IP application (for example BOOTP, TFTP). The Switch’s default IP
address is 10.90.90.90. You can change the default Switch IP address to meet the specification of your
networking address scheme.
The Switch is also assigned a unique MAC address by the factory. This MAC address cannot be changed,
but can be found on the initial boot console screen – shown below.
Figure 1–2 Boot Screen
The Switch’s MAC address can also be found in the Web management program on the Switch Information
Page 14
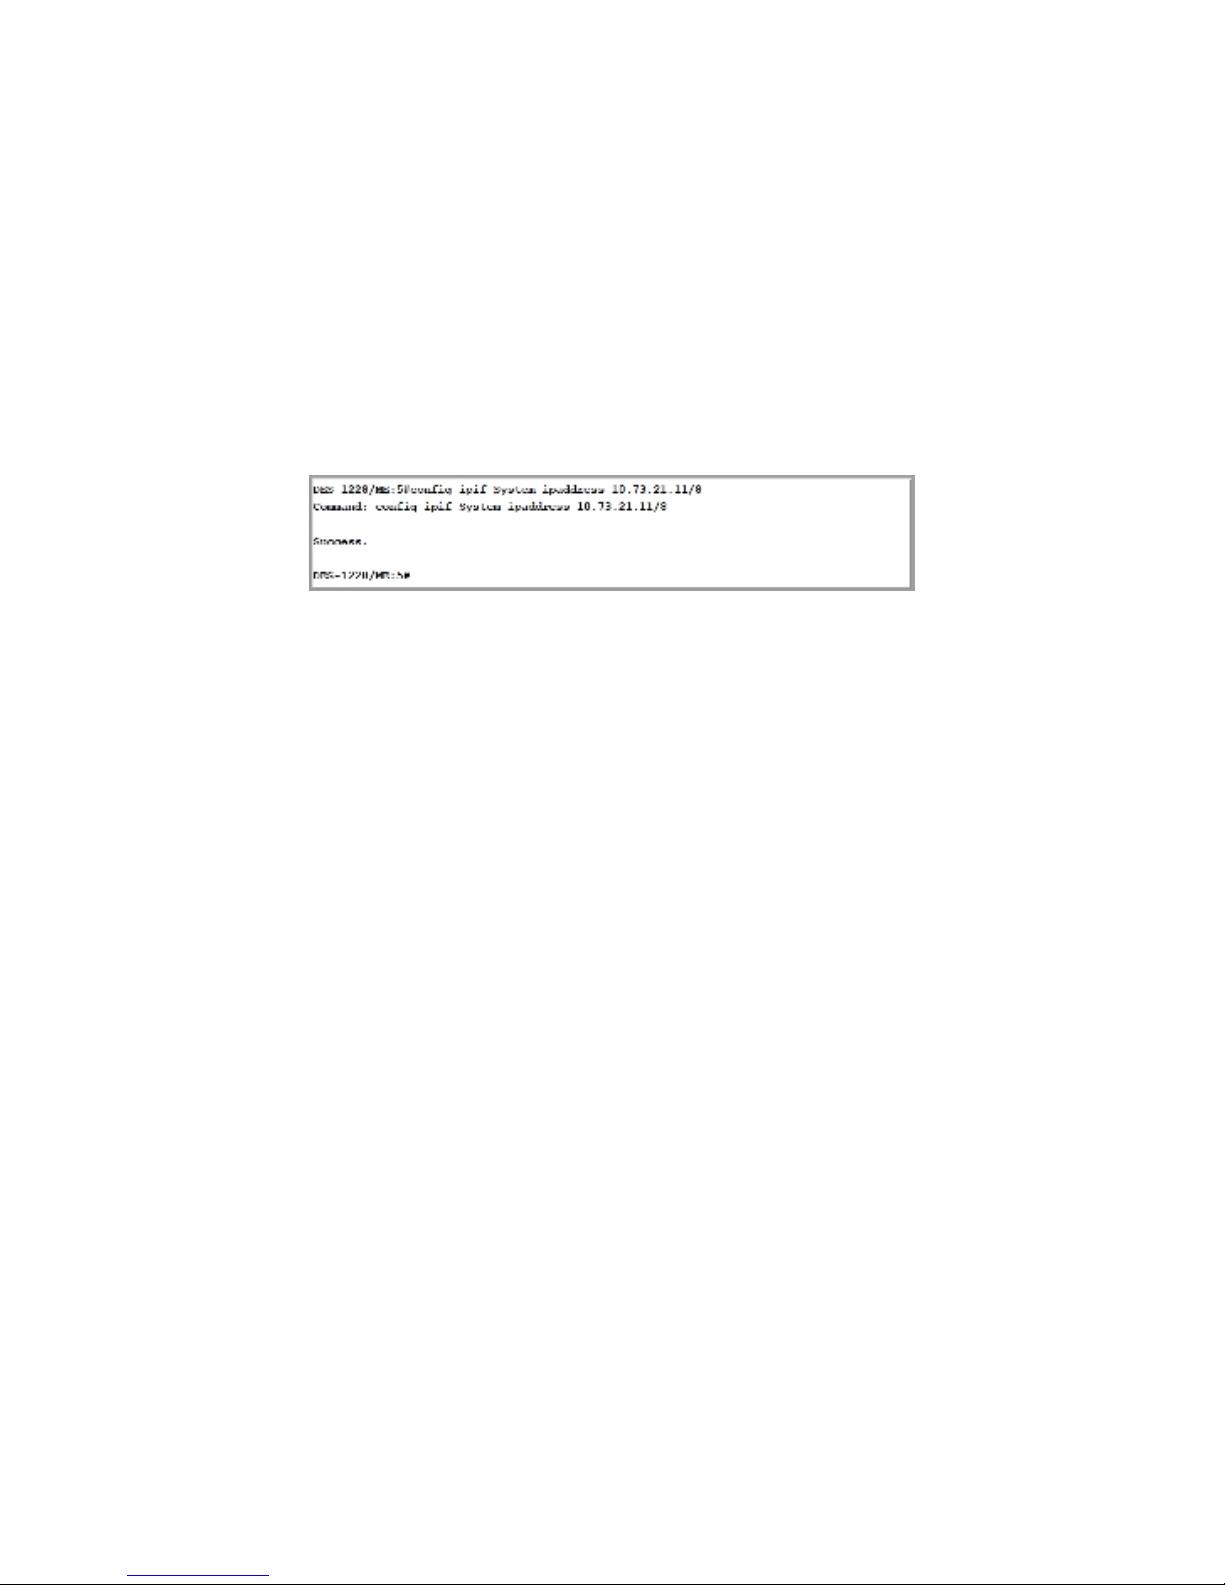
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
2
(Basic Settings) window in the Configuration folder.
The IP address for the Switch must be set before it can be managed with the Web-based manager. The Switch
IP address can be automatically set using BOOTP or DHCP protocols, in which case the actual address
assigned to the Switch must be known.
The IP address may be set using the Command Line Interface (CLI) over the console serial port as follows:
Starting at the command line prompt, enter the command config ipif System ipaddress
xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy. Where the x’s represent the IP address to be assigned to the IP interface
named System and the y’s represent the corresponding subnet mask.
Alternatively, users can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x’s represent the IP
address to be assigned to the IP interface named System and the z represents the corresponding number of
subnets in CIDR notation.
The IP interface named System on the Switch can be assigned an IP address and subnet mask which
can then be used to connect a management station to the Switch’s Telnet or Web-based management
agent.
Figure 1–3 Assigning an IP Address
In the above example, the Switch was assigned an IP address of 10.73.21.11 with a subnet mask of
255.0.0.0. The system message Success indicates that the command was executed successfully. The
Switch can now be configured and managed via Telnet, SNMP MIB browser and the CLI or via the Webbased management agent using the above IP address to connect to the Switch.
Page 15
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
3
2
22
2
USING THE CONSOLE CLI
The Switch supports a console management interface that allows the user to connect to the Switch’s
management agent via a serial port and a terminal or a computer running a terminal emulation program.
The console can also be used over the network using the TCP/IP Telnet protocol. The console program
can be used to configure the Switch to use a SNMP-based network management software over the
network.
This chapter describes how to use the console interface to access the Switch, change its settings, and
monitor its operation.
NOTE: Switch configuration settings are saved to non-volatile RAM using the save command.
The current configuration will then be retained in the Switch’s NV-RAM, and reloaded when the
Switch is rebooted. If the Switch is rebooted without using the save command, the last
configuration saved to NV-RAM is loaded.
Connecting to the Switch
The console interface is used by connecting the Switch to a VT100-compatible terminal or a computer
running an ordinary terminal emulator program (for example, the HyperTerminal program included with
the Windows operating system) using an RJ-45 serial cable. Your terminal parameters will need to be set
to:
• VT-100 compatible
• 9600 bps
• 8 data bits
• No parity
• One stop bit
• No flow control
The same functions may also be accessed over a Telnet interface. Once an IP address for the Switch has
been set, A Telnet program can be used (in VT-100 compatible terminal mode) to access and control the
Switch. All of the screens are identical, whether accessed from the console port or from a Telnet
interface.
After the Switch reboots and you have to logged in, the console looks like this:
Figure 2–1 Initial Console Screen after Logging In
Commands are entered at the command prompt, DES-1210-28/ME:5#
There are a number of helpful features included in the CLI. Entering the ? command displays a list of all
of the top-level commands.
Page 16
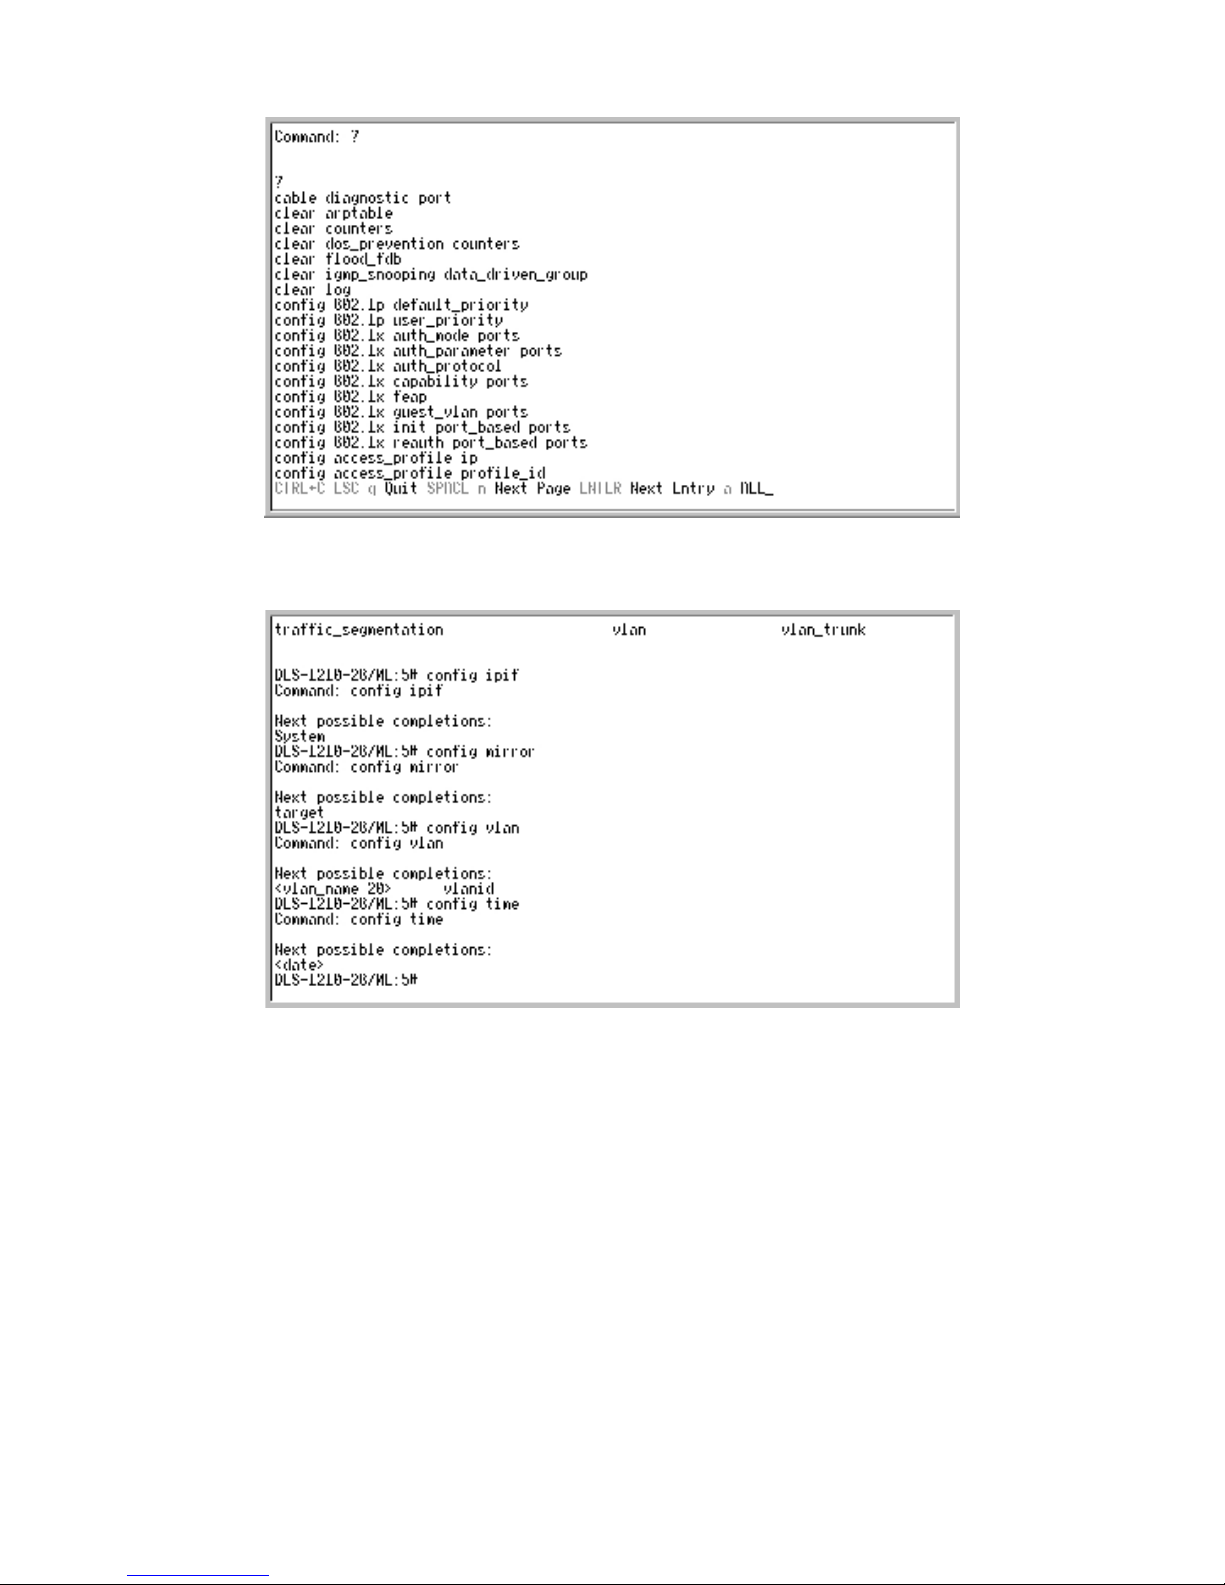
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
4
Figure 2–2 The ? Command
When entering a command without its required parameters, the CLI displays the prompt: command:
config account message and the options listed below.
Figure 2–3 Example Command Parameter Help
In this case, the command config account was entered with the parameter <username>. The CLI will then
prompt to enter the <username> with the message, command: config account. Every command in the
CLI has this feature, and complex commands have several layers of parameter prompting.
In addition, after typing any given command plus one space, users can see all of the next possible subcommands, in sequential order, by pressing the ? key.
To re-enter the previous command at the command prompt, press the up arrow cursor key. The previous
command appears at the command prompt.
Page 17
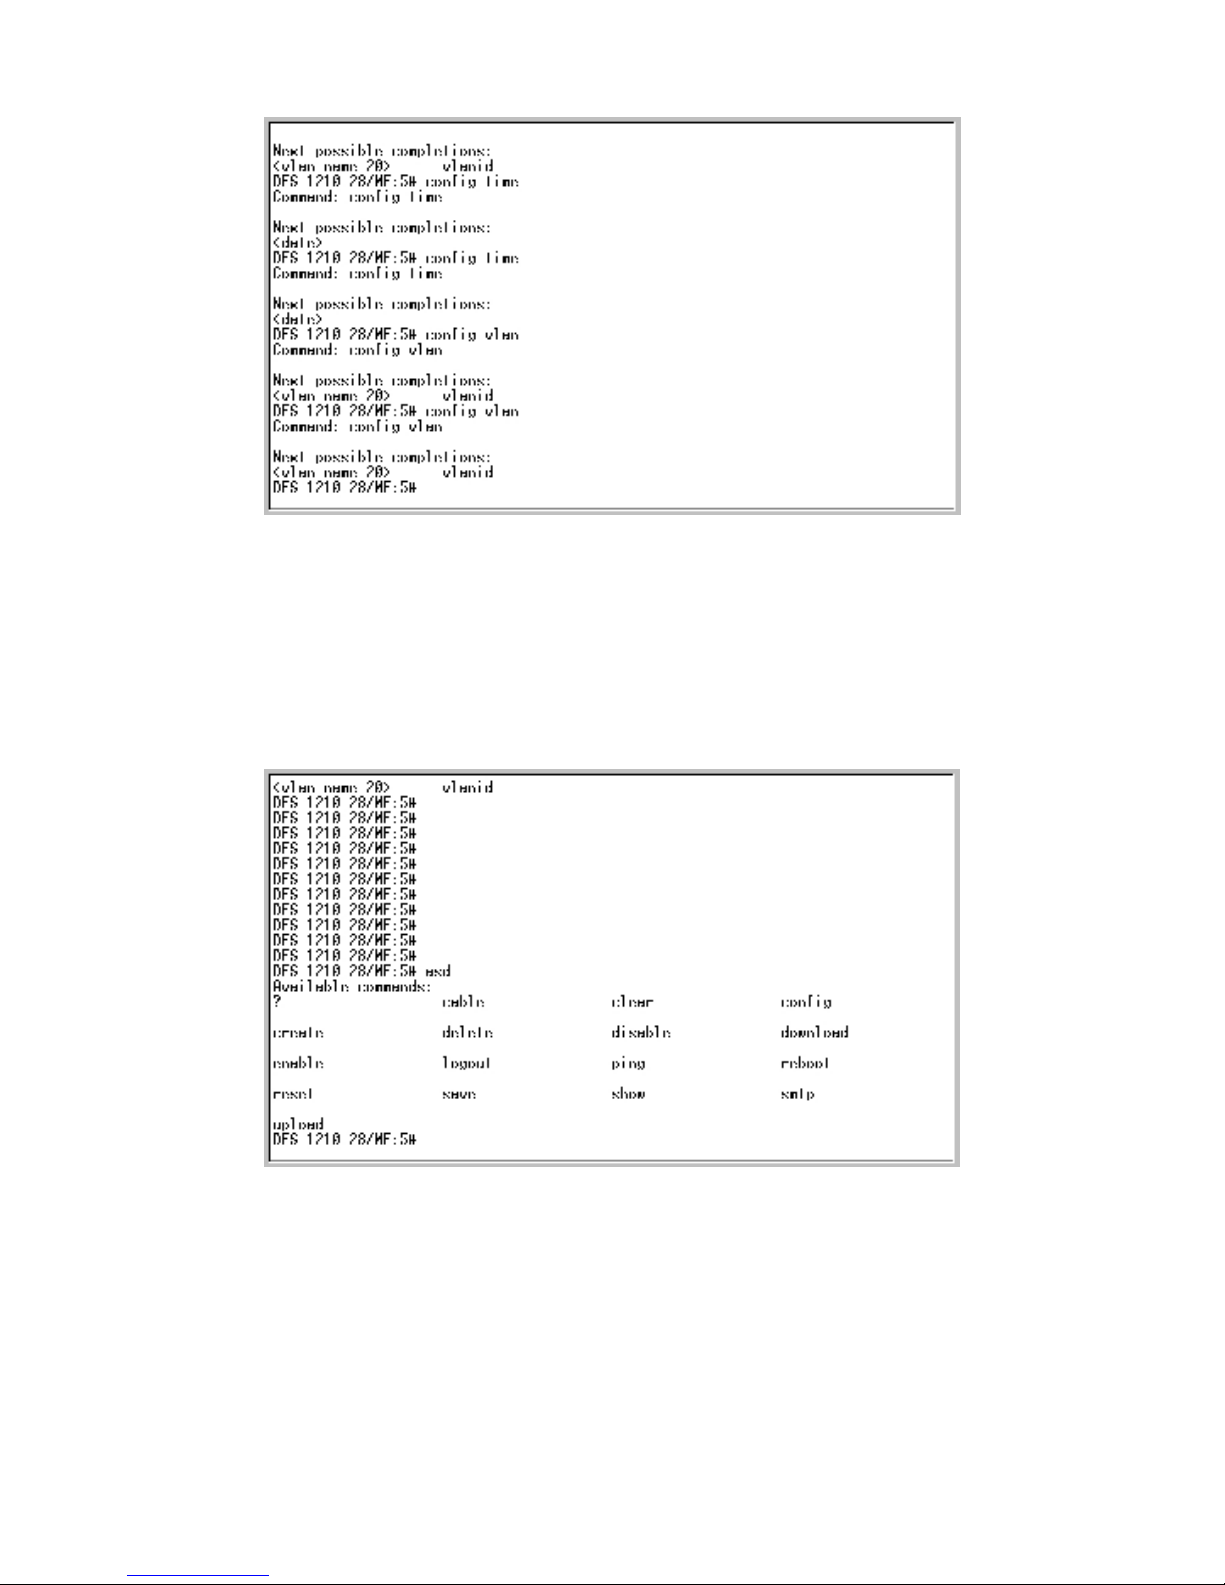
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
5
Figure 2–4 Using the Up Arrow to Re-enter a Command
In the above example, the command config account was entered without the required parameter
<username>, the CLI returned the command: config account prompt. The up arrow cursor control key
was pressed to re-enter the previous command (config account) at the command prompt. Now the
appropriate username can be entered and the config account command re-executed.
All commands in the CLI function in this way. In addition, the syntax of the help prompts are the same as
presented in this manual angle brackets < > indicate a numerical value or character string. The < > can
also indicate a word with a number for character allowed.
If a command is entered that is unrecognized by the CLI, the top-level commands are displayed under
the Available commands: prompt.
Figure 2–5 Available Commands
The top-level commands consist of commands such as show or config. Most of these commands
require one or more parameters to narrow the top-level command. This is equivalent to show what? or
config what? Where the what? is the next parameter.
For example, entering the show command with no additional parameters, the CLI will then display all of
the possible next parameters.
Page 18
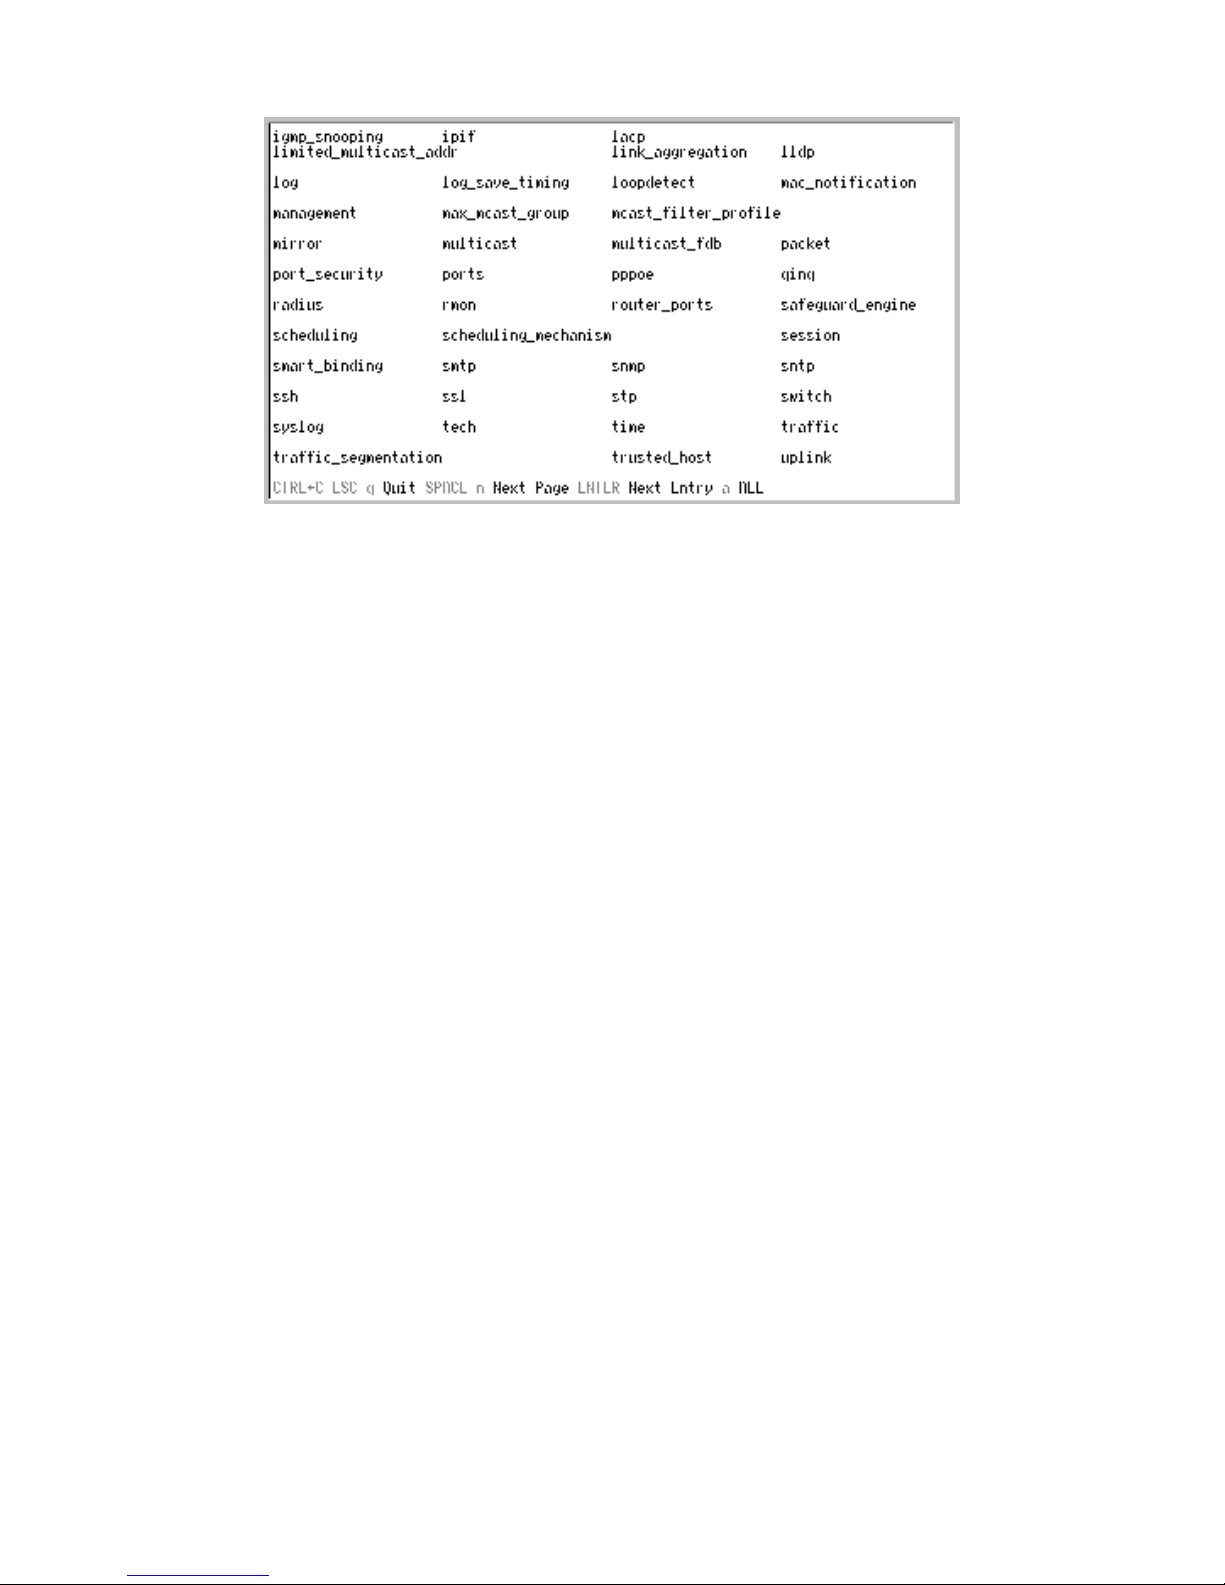
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
6
Figure 2–6 Next possible completions: Show Command
In the above example, all of the possible next parameters for the show command are displayed. At the
next command prompt in the example, the up arrow was used to re-enter the show command, followed
by the account parameter. The CLI then displays the user accounts configured on the Switch.
Page 19
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
7
3
33
3
COMMAND SYNTAX
The following symbols are used to describe how command entries are made and values and arguments
are specified in this manual. The online help contained in the CLI and available through the console
interface uses the same syntax.
NOTE: All commands are case-sensitive. Be sure to disable Caps Lock or any other unwanted
function that changes text case.
<angle brackets>
Purpose Encloses a variable or value that must be specified.
Syntax
create account [admin | oper |user] <username 15>
Description In the above syntax example, supply a username in the
<username> space. Do not type the angle brackets.
Example
Command
create account admin newadmin1
[square brackets]
Purpose Encloses a required value or set of required arguments. One value
or argument can be specified.
Syntax
create account [admin | oper |user] <username 15>
Description
In the above syntax example, specify admin, oper or a user level
account to be created. Do not type the square brackets.
Example
Command
create account user newuser1
| vertical bar
Purpose Separates two or more mutually exclusive items in a list, one of
which must be entered.
Syntax
create account [admin | oper | user] <username 15>
Description
In the above syntax example, specify admin, oper, or user. Do not
type the vertical bar.
Example
Command
create account user newuser1
All commands are case-sensitive. Be sure to disable Caps Lock or any other unwanted function that
changes text case.
Page 20
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
8
{braces}
Purpose Encloses an optional value or set of optional arguments.
Syntax reset
Description execute “reset” will return the switch to its factory default setting.
Example
command
reset
Please be aware that all configuration will be reset to default value.
Are you sure you want to proceed with system reset now? (Y/N)[N] N
Line Editing Key Usage
Delete Deletes the character under the cursor and then shifts the
remaining characters in the line to the left.
Backspace Deletes the character to the left of the cursor and then shifts the
remaining characters in the line to the left.
Insert or Ctrl+R Toggle on and off. When toggled on, inserts text and shifts previous
text to the right.
Left Arrow Moves the cursor to the left.
Right Arrow Moves the cursor to the right.
Up Arrow Repeats the previously entered command. Each time the up arrow
is pressed, the command previous to that displayed appears. This
way it is possible to review the command history for the current
session. Use the down arrow to progress sequentially forward
through the command history list.
Down Arrow The down arrow displays the next command in the command
history entered in the current session. This displays each command
sequentially as it was entered. Use the up arrow to review previous
commands.
Tab Shifts the cursor to the next field to the left.
Page 21
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
9
Multiple Page Display Control Keys
Space Displays the next page.
CTRL+c Stops the display of remaining pages when multiple pages are to be
displayed.
ESC Stops the display of remaining pages when multiple pages are to be
displayed.
n Displays the next page.
p Displays the previous page.
q Stops the display of remaining pages when multiple pages are to be
displayed.
r Refreshes the pages currently displayed.
a Displays the remaining pages without pausing between pages.
Enter Displays the next line or table entry.
Page 22
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
10
4
44
4
BASIC SWITCH COMMANDS
The Basic Switch commands in the Command Line Interface (CLI) are listed (along with the appropriate
parameters) in the following table.
Command Parameter
enable password
encryption
disable password
encryption
create account [admin | operator | user] <username 15>
config account <username 15>
show account
delete account <username 15>
show session
show switch
enable web <tcp_port_number 1-65535>
disable web
enable autoconfig
disable autoconfig
save {[config config_id <value 1-2> | log | account]}
reboot
reset {[config | system | account | password]} {force_agree}
logout
ping <ipaddr> {times <value 1-255>} {timeout <sec 1-99>}
enable telnet
disable telnet
show tech support
Each command is listed in detail, as follows:
enable password encryption
Purpose Used to enable password encryption on a user account.
Syntax
enable password encryption
Description The user account configuration information will be stored in the
configuration file, and can be applied to the system at a time in the
future. If the password encryption is enabled, the password will be in
encrypted form. If password encryption is disabled and the user
specifies the password in encrypted form, or if the password has
Page 23
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
11
been converted to encrypted form by the last enabled password
encryption command, the password will still be in encrypted form. It
can not revert back to plain text.
Parameters None.
Restrictions Only Administrator level users can issue this command.
Example usage:
To enable password encryption on the Switch:
DES-1210-28/ME:5# enable password encryption
Command: enable password encryption
Success.
DES-1210-28/ME:5#
disable password encryption
Purpose Used to disable password encryption on a user account.
Syntax
disable password encryption
Description The user account configuration information will be stored in the
configuration file, and can be applied to the system at a time in the
future. If the password encryption is enabled, the password will be in
encrypted form. If password encryption is disabled and the user
specifies the password in encrypted form, or if the password has
been converted to encrypted form by the last enabled password
encryption command, the password will still be in encrypted form. It
can not revert back to plain text.
Parameters None.
Restrictions Only Administrat level users can issue this command.
Example usage:
To disable password encryption on the Switch:
DES-1210-28/ME:5# disable password encryption
Command: disable password encryption
Success.
DES-1210-28/ME:5#
create account
Purpose To create user accounts.
Syntax
create account [admin | operator | user] <username 15>
Description
The create account command creates an administrator, operator,
or user account that consists of a username and an optional
Page 24
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
12
password. Up to 31 accounts can be created. You can enter
username and Enter. In this case, the system prompts for the
account’s password, which may be between 0 and 15 characters.
Alternatively, you can enter the username and password on the
same line.
Parameters
admin − Name of the administrator account.
oper − Specify an operator level account.
user − Specify a user account with read-only permissions.
<username 1-15> − The account username may be between 1 and
15 characters.
password <password_string> {encrypted} - the account password
can be included, and (optionally) can be encrypted.
Restrictions Only Administrator level users can issue this command.
Usernames can be between 1 and 15 characters.
Passwords can be between 0 and 15 characters.
NOTE: You are not required to enter a User Name. However, if you do not enter a User Name,
you cannot perform the following actions:
Create a monitor or operator (level 1 or level 14) users until an administrator user (level 15) is
defined.
Delete the last administrator user if there are monitor and/or operator users defined.
Example usage:
To create an administrator-level user account with the username ‘dlink’:
DES-1210-28/ME:5# create account admin dlink
Command: create account admin dlink
Enter a case-sensitive new password:*****
Enter the new password again for confirmation:*****
Success.
DES-1210-28/ME:5#
config account
Purpose To change the password for an existing user account.
Syntax
config account <username 15>
Description
The config account command changes the password for a user
account that has been created using the create account command.
The system prompts for the account’s new password, which may be
between 0 and 15 characters.
Parameters
<username 1-15> − the account username.
Restrictions Only Administrator-level users can issue this command.
Example usage:
To configure the user password of ‘dlink’ account:
Page 25
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
13
DES-1210-28/ME:5# config account dlink
Enter a old password:****
Enter a case-sensitive new password:******
Enter the new password again for confirmation:******
Success.
DES-1210-28/ME:5#
show account
Purpose To display information about all user accounts on the Switch.
Syntax
show account
Description
The show account command displays all account usernames and
their access levels created on the Switch. Up to 31 user accounts
can exist on the Switch at one time.
Parameters None.
Restrictions None.
Example usage:
To display the account which have been created:
DES-1210-28/ME:5# show account
Command: show account
Username Access Level
------------------ -----------dlink Admin
Total Entries : 1
DES-1210-28/ME:5#
delete account
Purpose To delete an existing user account.
Syntax
delete account <username 15>
Description
The delete account command deletes a user account that has been
created using the create account command.
Parameters
<username 15> − the account username.
Restrictions
Only Administrator-level users can issue this command.
Example usage:
To delete the user account ‘System’:
DES-1210-28/ME:5# delete account System
Command: delete account System
Page 26
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
14
Success.
DES-1210-28/ME:5#
show session
Purpose To display information about currently logged-in users.
Syntax
show session
Description
The show session command displays a list of all the users that are
logged-in at the time the command is issued. The information
includes the session ID (0 for the first logged-in user, 1 for the next
logged-in user, etc.), the Protocol used to connect to the Switch, the
user’s IP address, the user’s access Level (1=user, 15=admin), and
the account name on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display the way users logged in:
DES-1210-28/ME:5# show session
Command: show session
Total Entries: 1
ID Login Time Live Time From Level Name
-- -------------------- ------------ --------------- ----- --------------0 Jan 1 01:04:08 2011 00:11:05 Serial Port 14 dorothy
Total Entries: 1
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
show switch
Purpose To display information about the Switch.
Syntax
show switch
Description
The show switch command displays information about the Switch
settings, including Device Type, MAC Address, IP configuration,
Hardware/Software version, System information, and Switch
Network configuration.
Parameters None.
Restrictions None.
Example usage:
To display the Switch information:
Page 27
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
15
DES-1210-28/ME:5# show switch
Command: show switch
System name :
System Contact :
System Location :
System up time : 0 days, 1 hrs, 17 min, 19 secs
System Time : 01/01/2011 01:17:20
System hardware version :
System firmware version : 6.00.004
System boot version : 1.00.002
System Protocol version : 2.001.004
System serial number : 1MB1733K0000A
MAC Address : 00-B2-FD-DA-EE-EB
STP : Disabled
SNMP Status : Enabled
Port Mirroring : Disabled
802.1X Status : Disabled
Storm Control : Disabled
802.1Q Management VLAN : Disabled
Safeguard Engine : Enabled
IGMP Snooping : Disabled
DES-1210-28/ME:5#
enable web
Purpose To enable the HTTP-based management software on the Switch.
Syntax
enable web <tcp_port_number 1-65535>
Description
The enable web command enables the Web-based management
software on the Switch. The user can specify the TCP port number
the Switch uses to listen for Telnet requests.
Parameters
<tcp_port_number 1-65535> − The TCP port number. TCP ports are
numbered between 1 and 65535. The ‘well-known’ port for the Webbased management software is 80.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable HTTP and configure the TCP port number to listen for Telnet requests:
DES-1210-28/ME:5# enable web 80
Command: enable web 80
Success.
DES-1210-28/ME:5#
Page 28
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
16
disable web
Purpose To disable the HTTP-based management software on the Switch.
Syntax
disable web
Description
The disable web command disables the Web-based management
software on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable HTTP-based management software on the Switch:
DES-1210-28/ME:5# disable web
Command: disable web
Success.
DES-1210-28/ME:5#
enable autoconfig
Purpose Used to activate the auto configuration function for the Switch. This
will load a previously saved configuration file for current use.
Syntax
enable autoconfig
Description When autoconfig is enabled on the Switch, the DHCP reply will
contain a configuration file and path name. It will then request the file
from the TFTP server specified in the reply. When autoconfig is
enabled, the ipif settings will automatically become DHCP client.
Parameters None.
Restrictions When autoconfig is enabled, the Switch becomes a DHCP client
automatically (same as: config ipif System dhcp). The DHCP server
must have the TFTP server IP address and configuration file name,
and be configured to deliver this information in the data field of the
DHCP reply packet. The TFTP server must be running and have the
requested configuration file in its base directory when the request is
received from the Switch. Consult the DHCP server and TFTP
server software instructions for information on loading a
configuration file.
If the Switch is unable to complete the auto configuration process
the previously saved local configuration file present in Switch
memory will be loaded.
Example usage:
To enable auto configuration on the Switch:
DES-1210-28/ME:5# enable autoconfig
Command: enable autoconfig
Success.
DES-1210-28/ME:5#
Page 29
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
17
disable autoconfig
Purpose Use this to deactivate auto configuration from DHCP.
Syntax
disable autoconfig
Description
The disable autoconfig command is used to instruct the Switch not
to accept auto configuration instruction from the DHCP server. This
does not change the IP settings of the Switch. The ipif settings will
continue as DHCP client until changed with the config ipif command.
Parameters None.
Restrictions Only Administrator-level users can issue this command. .
Example usage:
To stop the auto configuration function:
DES-1210-28/ME:5# disable autoconfig
Command: disable autoconfig
Success.
DES-1210-28/ME:5#
show autoconfig
Purpose Used to display the current autoconfig status of the Switch.
Syntax
show autoconfig
Description
The show autoconfig command is used to list the current status of
the auto configuration function.
Parameters None.
Restrictions None.
Example usage:
To display the autoconfig status:
DES-1210-28/ME:5# show autoconfig
Command: show autoconfig
Autoconfig State: Enabled
DES-1210-28/ME:5#
save
Purpose To save changes in the Switch’s configuration to non-volatile RAM.
Syntax
save {[config config_id <value 1-2> | log | account]}
Description
The save command used to enter the current switch configuration
into non-volatile RAM. The saved switch configuration will be loaded
into the Switch’s memory each time the Switch is restarted.
Parameters
config – Used to save the current configuration to a file.
config_id <value 1-2> - Specifies which cfg file ID. if cfg ID is not
specified, it refers to the boot_up CFG file.
Page 30

DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
18
log – Used to save the current log to a file. The log file cannot be
deleted.
account – Used to save the account to a file.
Restrictions Only administrator-level users can issue this command.
Example usage:
To save the Switch’s current configuration to non-volatile RAM:
DES-1210-28/ME:5# save
Command: save
Building configuration ...
[OK]
DES-1210-28/ME:5#
reboot
Purpose To reboot the Switch. If the Switch is a member of a stack, it may be
rebooted individually, without affecting the other members of the
stack.
Syntax
reboot
Description
The reboot command restarts the Switch.
Parameters None.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To restart the Switch:
DES-1210-28/ME:5# reboot
Command: reboot
Are you sure you want to proceed with the system reboot?(y/n)y
% Please wait, the switch is rebooting...
DES-1210-28/ME:5# System will Reboot....
Boot Procedure
--------------------------------------------------------------------------------
Please wait, loading Runtime image ........................ 100%
MAC Address : 00-B2-FD-DA-EE-EB
H/W Version :
F/W Version : 6.00.004
--------------------------------------------------------------------------------
DES-1210-28/ME Fast Ethernet Switch
Command Line Interface
Page 31
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
19
Firmware: Build 6.00.004
Copyright(C) 2010 D-Link Corporation. All rights reserved.
DES-1210-28/ME login:
reset
Purpose To reset the Switch to the factory default settings.
Syntax
reset {[config | system | account | password]} {force_agree}
Description
The reset command restores the Switch’s configuration to the
default settings assigned from the factory. Execution of the reset
command through the CLI retains the unit’s current stack
membership number.
Parameters
config - If the keyword ‘config’ is specified, all of the factory default
settings are restored on the Switch including the IP address, user
accounts, and the switch history log. The Switch will not save or
reboot.
system − If the keyword ‘system’ is specified all of the factory default
settings are restored on the Switch. The Switch will save and reboot
after the settings are changed to default. Rebooting will clear all
entries in the Forwarding Data Base.
account − If the keyword ‘account is specified, all of the factory
default account settings are restored on the Switch.
password − If the keyword ‘password is specified, all of the factory
default password settings are restored on the Switch.
{force_agree} - When force_agree is specified, the reset command
will be executed immediately without further confirmation.
If no parameter is specified, the Switch’s current IP address, user
accounts, and the switch history log are not changed. All other
parameters are restored to the factory default settings. The Switch
will not save or reboot.
Restrictions Only administrator-level users can issue this command.
Example usage:
To restore all of the Switch’s parameters to their default values:
DES-1210-28/ME:5# reset system
Command: reset system
Are you sure you want to proceed with the system reset?(y/n)y
% Success.
DES-1210-28/ME:5# System will Reboot....
logout
Purpose To log out a user from the Switch’s console.
Syntax
Logout
Description
The logout command terminates the current user’s session on the
Page 32
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
20
Switch’s console.
Parameters None.
Restrictions None.
Example usage:
To terminate the current user’s console session:
DES-1210-28/ME:5# logout
ping
Purpose To test the connectivity between network devices.
Syntax
ping <ipaddr> {times <value 1-255>} {timeout <sec 1-99>}
Description
The ping command sends Internet Control Message Protocol
(ICMP) echo messages to a remote IP address. The remote IP
address then ‘echos’ or returns the message. This is used to confirm
connectivity between the Switch and the remote device.
Parameters
<ipaddr> - The IP address of the host.
times <value 1-255> - The number of individual ICMP echo
messages to be sent. The maximum value is 255. The default is 4.
timeout <sec 1-99> - The time-out period while waiting for a
response from the remote device. A value of 1 to 99 seconds can be
specified. The default is 1 second.
Restrictions None.
Example usage:
To ping the IP address 10.6.150.34 three times:
DES-1210-28/ME:5# ping 10.6.150.34 times 3
Command: ping 10.6.150.34 times 3
Reply Not Received From : 10.6.150.34, Timeout : 5 secs
Reply Not Received From : 10.6.150.34, Timeout : 5 secs
Reply Not Received From : 10.6.150.34, Timeout : 5 secs
--- 10.6.150.34 Ping Statistics --3 Packets Transmitted, 0 Packets Received, 100% Packets Loss
DES-1210-28/ME:5#
enable telnet
Purpose To enable the telnet.
Syntax
enable telnet
Description
The enable telnet command enables telnet.
Parameters None.
Restrictions Only Administrator or operate-level users can issue this command
Example usage:
To enable telnet:
DES-1210-28/ME:5# enable telnet
Page 33
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
21
Command: enable telnet
Success.
DES-1210-28/ME:5#
disable telnet
Purpose To disable telnet.
Syntax
disable telnet
Description
The disable telnet command disables telnet.
Parameters None.
Restrictions Only Administrator or operate-level users can issue this command
Example usage:
To disable telnet:
DES-1210-28/ME:5# disable telnet
Command: disable telnet
Success.
DES-1210-28/ME:5#
show tech support
Purpose To display system and configuration information. to provide to the
Technical Assistance Center when reporting a problem, use the
show tech-support command.
Syntax
show tech support
Description
The show tech support command displays system and
configuration information. to provide to the Technical Assistance
Center when reporting a problem.
By default, this command displays the output for technical-supportrelated show commands. Use keywords to specify the type of
information to be displayed. If you do not specify any parameters,
the system displays all configuration and memory data.
The show tech support command may time out if the configuration
file output takes longer to display than the configured session
timeout time. If this happens, enter a set logout timeout value of 0 to
disable automatic disconnection of idle sessions or enter a longer
timeout value.
The show tech support command output is continuous; it does not
display one screen at a time. To interrupt the output, press Esc.
Parameters None.
Restrictions Only Administrator-level users can issue this command..
Example usage:
To display technical support information on the Switch:
DES-1210-28/ME:5# show tech support
Page 34
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
22
Command: show tech support
- System Info. -
System name :
System Contact :
System Location :
System up time : 0 days, 1 hrs, 28 min, 24 secs
System Time : 01/01/2011 01:28:22
System hardware version :
System firmware version : 6.00.004
System boot version : 1.00.002
System Protocol version : 2.001.004
System serial number : 1MB1733K0000A
MAC Address : 00-B2-FD-DA-EE-EB
STP : Disabled
SNMP Status : Enabled
Port Mirroring : Disabled
802.1X Status : Disabled
Storm Control : Disabled
802.1Q Management VLAN : Disabled
Safeguard Engine : Enabled
IGMP Snooping : Disabled
CTRL+C ESC q Quit SPACE n Next Page ENTER Next Entry a ALL
Page 35
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
23
5
55
5
SMTP SERVER COMMANDS
The SMTP Server commands in the Command Line Interface (CLI) are listed (along with the appropriate
parameters) in the following table.
Command Parameter
enable smtp
disable smtp
config smtp
[self_mail_addr <mail_addr 64> | server <ipaddr> | server_port
<tcp_port_number 1-65535>] [{add mail_receiver <mail_addr 64>| delete
mail_receiver <index 1-8>}]
show smtp
smtp sent_testmsg
Each command is listed in detail, as follows:
enable smtp
Purpose To enable the SMTP server feature on the Switch.
Syntax
enable smtp
Description
The enable smtp command enables the SMTP server feature on
the Switch.
Parameters None.
Restrictions Only Administrator-level users can issue this command..
Example usage:
To enable SMTP feature on the Switch:
DES-1210-28/ME:5# enable smtp
Command: enable smtp
Success!
DES-1210-28/ME:5#
disable smtp
Purpose To disable the SMTP server feature on the Switch.
Syntax
disable smtp
Description
The disable smtp command disables the SMTP server feature on
the Switch.
Parameters None.
Restrictions Only Administrator-level users can issue this command..
Example usage:
To disable STMP feature on the Switch:
Page 36
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
24
DES-1210-28/ME:5# disable smtp
Command: disable smtp
Success!
DES-1210-28/ME:5#
config smtp
Purpose To configure the fields to set up the SMTP server for the switch,
along with setting e-mail addresses to which switch log files can be
sent when a problem arises on the Switch.
Syntax
config smtp [self_mail_addr <mail_addr 64> | server <ipaddr> |
server_port <tcp_port_number 1-65535>] [{add mail_receiver
<mail_addr 64>| delete mail_receiver <index 1-8>}]
Description
The config smtp command is used to configure the fields to set up
the SMTP server for the switch, along with setting e-mail addresses
to which switch log files can be sent when a problem arises on the
Switch.
Parameters
self_mail_addr <mail_addr 64> − Specifies the e-mail address from
which mail messages will be sent. Only one self mail address can be
configured on the Swtich.
server <ipaddr> − Specifies the IP address of the SMTP server. This
will be the device that sends out the mail for user. For example,
10.90.90.99.
<tcp_port_number 1-65535> − Specifies the port number that the
Switch will connect with on the SMTP server. The range is between
1 and 65535.
add mail_receiver <mail_addr 64> − Specifies a list of e-mail
addresses so recipients can receive e-mail messages regarding
Switch functions. Up to 8 e-mail address can be added per Switch.
delete mail_receiver <index 1-8> − Specifies the e-mail address
index to be deleted.
Restrictions Only Administrator-level users can issue this command..
Example usage:
To config SMTP with self mail address ‘[email protected]’ on the Switch:
DES-1210-28/ME:5# config smtp self_mail_addr [email protected]
Command: config smtp self_mail_addr [email protected]
Success!
DES-1210-28/ME:5#
show smtp
Purpose To display the SMTP server settings on the Switch.
Syntax
show smtp
Description
The show smtp command displays the SMTP server settings on the
Switch.
Parameters None.
Page 37
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
25
Restrictions None.
Example usage:
To display SMTP information on the Switch:
DES-1210-28/ME:5# show smtp
Command: show smtp
smtp status : Enable
smtp server address : 0.0.0.0
smtp server port : 25
self mail address : [email protected]
Index Mail Receiver Address
-------- -------------------------------------1
2
3
4
5
6
7
8
DES-1210-28/ME:5#
smtp sent_testmsg
Purpose To send test messages to all mail recipients configured on the
Switch.
Syntax
smtp sent_testmsg
Description
The smtp sent_testmsg command is used to send test messages
to all mail recipients configured on the Switch.
Parameters None.
Restrictions Only Administrator-level users can issue this command..
Example usage:
To send SMTP test message to all mail receivers:
DES-1210-28/ME:5# smtp sent_testmsg
Command: smtp sent_testmsg
Subject: This is a SMTP test
Content: Hello everybody!!
Sending mail, please wait...
Success!
DES-1210-28/ME:5#
Page 38
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
26
6
66
6
MODIFY BANNER AND PROMPT COMMANDS
The Modify Banner and Prompt commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
config
command_prompt
[<string 32> | default | username]
config
greeting_message
{default}
show
greeting_message
Each command is listed in detail, as follows:
config command_prompt
Purpose To configure the command prompt.
Syntax
config command_prompt [<string 32> | default | username]
Description
The config command_prompt command configures the command
prompt.
Parameters
<string 32> – The command prompt can be changed by entering a
new name of no more that 32 characters.
default – The command prompt will reset to factory default command
prompt. Default = the name of the Switch model, for example “DES1210-28”.
username – The command prompt will be changed to the login
username.
Restrictions
Only Administrator-level users can issue this command. Other
restrictions include:
If the “reset” command is executed, the modified command prompt
will remain modified. However, the “reset config/reset system”
command will reset the command prompt to the original factory
banner.
Example usage:
To modify the command prompt to “AtYourService”:
DES-1210-28/ME:5# config command_prompt AtYourService
Command: config command_prompt AtYourService
Success.
AtYourService:5#
Page 39
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
27
config greeting_message
Purpose Used to configure the login banner (greeting message).
Syntax
config greeting_message {default}
Description
The config greeting_message command to modify the login
banner (greeting message).
Parameters
default – If the user enters default to the modify banner command,
then the banner will be reset to the original factory banner.
To open the Banner Editor, click Enter after typing the config
greeting_message command. Type the information to be displayed
on the banner by using the commands described on the Banner
Editor:
Quit without save: Ctrl+C
Save and quit: Ctrl+W
Move cursor: Left/Right/Up/Down
Delete line: Ctrl+D
Erase all setting: Ctrl+X
Reload original setting: Ctrl+L
Restrictions
Only Administrator-level users can issue this command. Other
restrictions include:
If the “reset” command is executed, the modified banner will remain
modified. However, the “reset config/reset system” command will
reset the modified banner to the original factory banner.
The capacity of the banner is 6*80. 6 Lines and 80 characters per
line.
Ctrl+W will only save the modified banner in the DRAM. Users need
to type the “save config/save all” command to save it into Flash.
Only valid in threshold level.
Example usage:
To the banner:
Page 40
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
28
DES-1210-28/ME:5#
Command: config greeting_message
Greeting Messages Editor
===========================================================
DES-1210-28/ME Fast Ethernet Switch
Command Line Interface
Copyright(C) 2012 D-Link Corporation. All rights reserved.
============================================================
<Function Key> <Control Key>
Ctrl+C Quit without save left/right/
Ctrl+W Save and quit up/down Move cursor
Ctrl+D Delete line
Ctrl+X Erase all setting
Ctrl+L Reload original setting
show greeting_message
Purpose Used to view the currently configured greeting message configured
on the Switch.
Syntax
show greeting_message
Description
The show greeting_message command is used to view the
currently configured greeting message on the Switch.
Parameters None.
Restrictions None.
Example usage:
To view the currently configured greeting message:
DES-1210-28/ME:5# show greeting_message
Command: show greeting_message
DES-1210-28/ME Fast Ethernet Switch
Command Line Interface
Copyright(C) 2012 D-Link Corporation. All rights reserved.
DES-1210-28/ME:5#
Page 41
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
29
7
77
7
SWITCH PORT COMMANDS
The Switch Port commands in the Command Line Interface (CLI) are listed (along with the appropriate
parameters) in the following table.
Command Parameter
config ports
config ports [all | <portlist>] medium_type [copper | fiber_100 | fiber_1G]
MDI/MDIX [MDI | MDIX | auto] {description <desc 32> | flow_control [enable |
disable] | learning [enable | disable] | state [enable | disable] | speed [auto |
10_half | 100_full | 100_half | 10_full | 10_half]}
show ports
{<portlist> | all} {description | err_disabled}
Each command is listed in detail, as follows:
config ports
Purpose To configure the Switch’s Ethernet port settings.
Syntax
config ports [all | <portlist>] medium_type [copper | fiber_100 |
fiber_1G] MDI/MDIX [MDI | MDIX | auto] {description <desc 32> |
flow_control [enable | disable] | learning [enable | disable] |
state [enable | disable] | speed [auto | 10_half | 100_full |
100_half | 10_full | 10_half]}
Description
The config ports command configures the Switch’s Ethernet port
settings. Only the ports listed in the <portlist> are affected.
Parameters
<portlist> − A port or range of ports to be configured.
all − Configures all ports on the Switch.
medium_type [copper | fiber_100 | fiber_1G ] − If configuring the
Combo ports, this defines the type of medium being configured.
MDI/MDIX [MDI | MDIX | j auto] − Specifies the MDI or MDIX setting
of the port. The MDIX setting can be auto, normal or cross.
If set to normal state, the port in MDIX mode, can be connected to
PC NIC using a straight cable. If set to cross state, the port in mdi
mode, can be connected to a port (in mdix mode) on another switch
through a straight cable.
description <desc 32> − Enter and alphanumeric string of no more
that 32 characters to describe a selected port interface.
flow_control [enable] – Enables flow control for the specified ports.
flow_control [disable] – Disables flow control for the specified ports.
learning [enable | disable] c Enables or disables the MAC address
learning on the specified range of ports.
state [enable | disable] − Enables or disables the specified range of
ports.
speed – Sets the speed of a port or range of ports, with the addition
of one of the following:
• auto − Enables auto-negotiation for the specified range of
ports.
Page 42
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
30
• [10 | 100 | 1000] − Configures the speed in Mbps for the
specified range of ports.
• [half | full] − Configures the specified range of ports as either
full or half-duplex.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To configure the speed of ports 1-3 to be 100 Mbps, full duplex, learning and state enabled:
DES-1210-28/ME:5# config ports 1-3 medium_type copper speed 100_full learning en
able state enable
Command: config ports 1-3 medium_type copper speed 100_full learning enable stat
e enable
Success
DES-1210-28/ME:5#
show ports
Purpose To display the current configuration of a range of ports.
Syntax
show ports {<portlist> | all} {description | err_disabled}
Description
The show ports command displays the current configuration of a
port or range of ports.
Parameters
<portlist> − A port or range of ports whose settings are to be
displayed.
all – Specifies all ports to be displayed.
Restrictions None.
Example usage:
To display the configuration of port 8 on the Switch:
DES-1210-28/ME:5# show ports 8
Command: show ports 8
Port State/ Settings Connection Address
Type MDI Speed/Duplex/FlowCtrl Speed/Duplex/FlowCtrl Learning
----- ------- -------------------------------- --------------------------------- -----------8 Enabled Auto/Disabled Link Down Enabled
Auto
DES-1210-28/ME:5#
Page 43
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
31
8
88
8
LOOPBACK DETECTION COMMANDS
The Loopback Detection commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
config loopdetect [enable | disable]
config loopdetect mode [portbase | vlanbase]
config loopdetect ports [<portlist> | all] [enable | disable]
config loopdetect interval_time <value 1-32767> lbd_recover_time [0 | <value 60-1000000>]
show loopdetect {ports [<portlist> | all]}
Each command is listed in detail, as follows:
config loopdetect
Purpose To enable the loop back detection to be enabled or disabled on the
Switch.
Syntax
config loopdetect [enable | disable]
Description
The config loopdetect command enables or disables the loop back
detection on the Switch.
Parameters
[enabled | disabled] − Specifies the loop back detection is enabled or
disabled on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To enable the loopback detection feature on the Switch:
DES-1210-28/ME:5# config loopdetect enable
Command: config loopdetect enable
Success!
DES-1210-28/ME:5#
config loopdetect mode
Purpose To configure the loop back detection mode to be portbase or
vlanbase on the Switch.
Syntax
config loopdetect mode [portbase | vlanbase]
Description
The config loopdetect mode command configures loop back
detection mode to be portbase or vlanbase on the Switch.
Parameters
[portbase | vlanbase]] - Specifies the loopdetect mode to be
portbase or vlanbase.
Page 44
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
32
Restrictions None.
Example usage:
To configure the loopback detection mode to be portabse on the Switch:
DES-1210-28/ME:5# config loopdetect mode portbase
Command: config loopdetect mode portbase
Success!
DES-1210-28/ME:5#
config loopdetect ports
Purpose To configures the loop back detection to be enabled or disabled for
the specific ports on the Switch.
Syntax
config loopdetect ports [<portlist> | all] [enable | disable]
Description
The config loopdetect ports command configures the loop back
detection to be enabled or disabled for the specific ports on the
Switch.
Parameters
<portlist> − A port or range of ports to be configured.
all − All ports settings are to be configured.
[enabled | disabled] − Specifies the loop back detection is enabled or
disabled for the specified ports on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To enable the loop back detection on the Switch:
DES-1210-28/ME:5# config loopdetect ports all enable
Command: config loopdetect ports all enable
Success!
DES-1210-28/ME:5#
config loopdetect
Purpose To configure the loop back detection interval time and recover time
on the Switch.
Syntax
config loopdetect interval_time <value 1-32767>
lbd_recover_time [0 | <value 60-1000000>]
Description
The config loopdetect command configures the loop back
detection interval time and recover time on the Switch.
Parameters
interval_time <value 1-32767> − Specifies the interval time of loop
back detection. The range is between 1 and 32767 seconds.
lbd_recover_time [0 | <value 60-10000>] − Specifies the recover
time of loop back detection on the switch. The range is between 60
and 10000 seconds.
Restrictions Only administrator or operate-level users can issue this command.
Page 45
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
33
Example usage:
To configure the loop back detection with interval time 500 on the Switch:
DES-1210-28/ME:5# config loopdetect interval_time 500
Command: config loopdetect interval_time 500
Success!
DES-1210-28/ME:5#
show loopdetect
Purpose To display the loop back detection information on the Switch.
Syntax
show loopdetect {ports [<portlist> | all]}
Description
The show loopdetect command displays the loop back detection
information on the Switch.
Parameters
<portlist> − A port or range of ports to be displayed.
all − All ports settings are to be displayed.
Restrictions None.
Example usage:
To display the loop back detection information on the Switch:
DES-1210-28/ME:5# show loopdetect
Command: show loopdetect
Loopdetect Global Settings
---------------------------------Loopdetect Status : Enabled
Loopdetect Mode : Port-Base
Loopdetect Interval : 100
Recover Time : 60
DES-1210-28/ME:5#
Page 46
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
34
9
99
9
DOS PREVENTION COMMANDS
The DoS Prevention commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
config dos_prevention
dos_type
[ {land_attack | blat_attack | smurf_attack | tcp_null_scan | tcp_xmascan |
tcp_synfin | tcp_syn_srcport_less_1024} | all] {action [ drop | mirror <portlist>
{priority <value 0-7> | rx_rate [ no_limit | <value 64-1024000> ] } ] | enable |
disable ] }
show dos_prevention
{ land_attack | blat_attack | smurf_attack | tcp_null_scan | tcp_xmascan |
tcp_synfin | tcp_syn_srcport_less_1024 }
clear dos_prevention
counters
[land_attack | blat_attack | smurf_attack | tcp_null_scan | tcp_xmascan |
tcp_synfin | tcp_syn_srcport_less_1024]
enable dos_prevention
trap_log
disable dos_prevention
trap_log
Each command is listed in detail, as follows:
config dos_prevention dos_type
Purpose Used to discard the L3 control packets sent to CPU from specific
ports.
Syntax
config dos_prevention dos_type [ {land_attack | blat_attack |
smurf_attack | tcp_null_scan | tcp_xmascan | tcp_synfin |
tcp_syn_srcport_less_1024} | all] {action [ drop | mirror
<portlist> {priority <value 0-7> | rx_rate [ no_limit | <value 641024000> ] } ] | enable | disable ] }
Description
The create snmp user command is used to configure the
prevention of DoS attacks, and includes state and action. The
packets matching will be used by the hardware. For a specific type
of attack, the content of the packet, regardless of the receipt port or
destination port, will be matched against a specific pattern.
Parameters The type of DoS attack. Possible values are as follows:
land_attack, blat_attack, smurf_attack, tcp_null_scan, tcp_xmascan
tcp_synfin and tcp_syn_srcport_less_1024.
state - Enable or disable DoS prevention.
By default, prevention for all types of DoS are enabled except for
tcp_syn_srcport_less_1024.
action - When enabling DoS prevention, the following actions can be
taken.
drop – Drop the attack packets.
mirror – Mirror the packet to other port for further process.
Page 47
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
35
priority – Change packet priority by the Switch from 0 to 7.
If the priority is not specified, the original priority will be used.
rx_rate – controls the rate of the received DoS attack packets.
• If not specified, the default action is drop.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To configure a land attack and blat attack prevention:
DES-1210-28/ME:5# config dos_prevention dos_type blat_attack action
drop
Command: config dos_prevention dos_type blat_attack action drop
Success!
DES-1210-28/ME:5#
show dos_prevention
Purpose Used to display DoS prevention information.
Syntax
show dos_prevention { land_attack | blat_attack | smurf_attack |
tcp_null_scan | tcp_xmascan | tcp_synfin |
tcp_syn_srcport_less_1024 }
Description
The show dos_prevention command is used to display DoS
prevention information, including the type of DoS attack, the
prevention state, the corresponding action if the prevention is
enabled, and the counter information of the DoS packet.
Parameters The type of DoS attack. Possible values are as follows:
land_attack, blat_attack, smurf_attack, tcp_null_scan, tcp_xmascan
tcp_synfin and tcp_syn_srcport_less_1024.
Restrictions None.
Example usage:
To display DoS prevention information:
DES-1210-28/ME:5# show dos_prevention
Command: show dos_prevention
DosType State Action Frame Counts
Land Attack Disabled Mirror 0
Blat Attack Disabled Mirror 0
Smurf Attack Disabled Mirror 0
Tcp Null Scan Disabled Mirror 0
Tcp Xmascan Disabled Mirror 0
Tcp Synfin Disabled Mirror 0
Tcp Syn Srcport less 1024 Disabled Mirror 0
Success!
DES-1210-28/ME:5#
Page 48
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
36
To display DoS prevention information for Land Attack:
DES-1210-28/ME:5# show dos_prevention land_attack
Command: show dos_prevention land_attack
DoS Type: Land Attack
State: Disabled
Action: Mirror
Port: 7
Priority: 5
Rx Rate(Kbit/sec): 1024
Frame Counts: 0
Success!
DES-1210-28/ME:5#
clear dos_prevention counters
Purpose Used to clear the counters of the prevention of each DoS attack.
Syntax
clear dos_prevention counters [land_attack | blat_attack |
smurf_attack | tcp_null_scan | tcp_xmascan | tcp_synfin |
tcp_syn_srcport_less_1024]
Description
The clear dos_prevention counters command is used to clear the
counters of the prevention of each DoS attack.
Parameters The type of DoS attack. Possible values are as follows:
land_attack, blat_attack, smurf_attack, tcp_null_scan, tcp_xmascan
tcp_synfin and tcp_syn_srcport_less_1024.
Restrictions Only Administrator-level users can issue this command.
Example usage:
To clear all counters of the prevention of each smurf attack:
DES-1210-28/ME:5# clear dos_prevention counters smurf_attack
Command: clear dos_prevention counters smurf_attack
DES-1210-28/ME:5#
enable dos_prevention trap_log
Purpose Used to enable a DoS prevention trap/log.
Syntax
enable dos_prevention trap_log
Description
The enable dos_prevention trap_log command is used to send
traps and logs when a DoS attack event occurs. The event will be
logged only when the action is specified as drop.
Parameters None.
Restrictions Only Administrator-level users can issue this command.
Example usage:
To enable a DoS prevention trap/log:
Page 49
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
37
DES-1210-28/ME:5# enable dos_prevention trap_log
Command: enable dos_prevention trap_log
DES-1210-28/ME:5#
disable dos_prevention trap_log
Purpose Used to disable a DoS prevention trap/log.
Syntax
disable dos_prevention trap_log
Description
The disable dos_prevention trap_log command is used to disable
a DoS prevention trap/log.
Parameters None.
Restrictions Only Administrator-level users can issue this command.
Example usage:
To disable a DoS prevention trap/log:
DES-1210-28/ME:5# disable dos_prevention trap_log
Command: disable dos_prevention trap_log
DES-1210-28/ME:5#
Page 50
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
38
10
1010
10
PPPOE CIRCUIT ID INSERTION COMMANDS
PPPoE Circuit ID Insertion is used to produce the unique subscriber mapping capability that is possible
on ATM networks between ATM-DSL local loop and the PPPoE server. The PPPoE server will use the
inserted Circuit Identifier sub-tag of the received packet to provide AAA services (Authentication,
Authorization and Accounting). Through this method, Ethernet networks can be as the alternative of the
ATM networks.
The PPPoE Circuit ID Insertion commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
config pppoe circuit_id
_insertion state
[enable | disable]
config pppoe
circuit_id_insertion
ports
[ circuit_id [ mac | ip | udf <string 32> ] | state [enable | disable ] ]
show pppoe
circuit_id_insertion
show pppoe
circuit_id_insertion
ports
{<portlist>}
Each command is listed in detail, as follows:
config pppoe circuit_id_insertion state
Purpose Used to enable or disable the PPPoE circuit identifier insertion.
Syntax
config pppoe circuit_id_insertion state [enable | disable]
Description When PPPoE circuit identifier insertion is enabled, the system will
insert the circuit ID tag to the received PPPoE discover and request
packet if the tag is absent, and remove the circuit ID tag from the
received PPPoE offer and session confirmation packet.
The inserted circuit ID contains the following information:
Client MAC address
Device ID
Port number
By default, the Switch IP address is used as the device ID to encode
the circuit ID option.
Parameters
[enable | disable] – Enables or disable PPPoE circuit ID insertion
globally. The function is disabled by default.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To globally enable PPPoE circuit identifier insertion:
DES-1210-28/ME:5# config pppoe circuit_id_insertion state enable
Command: config pppoe circuit_id_insertion state enable
Page 51
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
39
Success.
DES-1210-28/ME:5#
config pppoe circuit_id_insertion ports
Purpose Used to enable and disable PPPoE circuit identifier insertion on a
per port basis and specify how to encode the circuit ID option.
Syntax
config pppoe circuit_id_insertion ports <portlist> [ circuit_id
[ mac | ip | udf <string 32> ] | state [enable | disable ] ]
Description When the port’s state and the global state are enabled, the system
will insert the Circuit ID TAG to the received PPPoE discovery
initiation and request packet if the TAG is absent, and remove the
Circuit ID tag, inserted by the system, from the received PPPoE offer
and session confirmation packet.
Parameters
<portlist> – Specifies a list of ports to be configured.
The default settings are enabled for ID insertion per port, but
disabled globally.
circuit_id – Configures the device ID used for encoding of the circuit
ID option.
mac – Specifies that the Switch MAC address be used to encode the
circuit ID option.
ip – Specifies that the Switch IP address be used to encode the
circuit ID option.
udf – A user defined string to be used to encode the circuit ID option.
The maximum length is 32.
The default encoding for the device ID option is the Switch IP
address.
state – Specify to enable or disable PPPoE circuit ID insertion for the
ports listed.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To enable port 1~5 PPPoE circuit ID insertion function and use Host MAC:
DES-1210-28/ME:5# config pppoe circuit_id_insertion ports 1-5 circuit_id
mac state enable
Command: config pppoe circuit_id_insertion ports 1-5 circuit_id mac
state enable
Success.
DES-1210-28/ME:5#
show pppoe circuit_id_insertion
Purpose Used to display the PPPoE circuit identifier insertion status for the
Switch.
Syntax
show pppoe circuit_id_insertion
Description
The show pppoe circuit_id_insertion command is used to display
Page 52
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
40
the global state configuration of the PPPoE circuit ID insertion
function.
Parameters None.
Restrictions None.
Example usage:
To view the global PPPoE ID insertion state:
DES-1210-28/ME:5# show pppoe circuit_id_insertion
Command: show pppoe circuit_id_insertion
Status: Enabled
DES-1210-28/ME:5#
show pppoe circuit_id_insertion ports
Purpose Used to display the PPPoE ID insertion configuration on a per
port basis.
Syntax
show pppoe circuit_id_insertion ports {<portlist>}
Description
The show pppoe circuit_id_insertion ports command allows
the user to view the configuration of PPPoE ID insertion for each
port.
Parameters
<portlist> - Specifies which ports to display. If no ports are
specified, all ports configuration will be listed.
Restrictions None.
Example usage:
To view the PPPoE circuit ID configuration for ports 2 to 5:
DES-1210-28/ME:5# show pppoe circuit_id_insertion ports 2-5
Command: show pppoe circuit_id_insertion ports 2-5
Port State Cirucit ID
---- -------- --------------------------------------------2 Enabled Switch MAC
3 Enabled Switch MAC
4 Enabled Switch MAC
5 Enabled Switch MAC
DES-1210-28/ME:5#
Page 53
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
41
11
1111
11
DHCP SERVER SCREENING COMMANDS
The DHCP server screenint commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Due to this function allow you not only to restrict all DHCP Server packets but also to receive any
specified DHCP server packet by any specified DHCP client, it is useful when one or more than one
DHCP servers are present on the network and both provide DHCP services to different distinct groups of
clients.
When DHCP Server Screening function is enabled, all DHCP Server packets will be filtere from a specif ic
port. Also, you are allow to create entries for specific Server IP address an d Client MAC address bi
nding by por t-based. Be aware th a tthe DHCP Ser ver Screen ing f uncti n must b e enabled first On ce
all sett ng is do ne, all DHC P Serve packe s wi ll be filtered fro m a speci fic port e cep t those tha meet
th e Se ver IP Ad dres s and Cli ent M AC Addres s binding .
Command Parameter
config filter
dhcp_server
[add permit server_ip <ipaddr> { client_mac <macaddr>} ports [ <portlist> | all ] |
delete permit server_ip <ipaddr> { client_mac <macaddr> } ports [ <portlist> | all ]
| ports [ <portlist> | all ] state [ enable | disable]]
show filter dhcp_server
config dhcp_server
screening ports
<portlist> state [enable | disable]
show dhcp_server
screening
Each command is listed in detail, as follows:
config filter dhcp_server
Purpose DHCP server packets except those that have been IP/client MAC
bound will be filtered. This command is used to configure the state of
the function for filtering of DHCP server packet and to add/delete the
DHCP server/client binding entry.
Syntax
config filter dhcp_server [add permit server_ip <ipaddr>
{ client_mac <macaddr>} ports [ <portlist> | all ] | delete permit
server_ip <ipaddr> { client_mac <macaddr> } ports [ <portlist> |
all ] | ports [ <portlist> | all ] state [ enable | disable]]
Description
The config filter dhcp_server command has two purposes: To filter
all DHCP server packets on the specified port(s) and to allow some
DHCP server packets to forwarded if they are on the pre-defined
server IP address/MAC address binding list. Thus the DHCP server
can be restricted to service a specified DHCP client. This is useful
when there are two or more DHCP servers present on f network.
Parameters
<ipaddr> – The IP address of the DHCP server to be filtered
<macaddr> – The MAC address of the DHCP client.
state – Enable/Disable the DHCP filter state
ports <portlist> – The port number to which the DHCP filter will be
applied.
Page 54
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
42
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To add an entry from the DHCP server/client filter list in the Switch’s database:
DES-1210-28/ME:5# config filter dhcp_server add permit server_ip
10.1.1.1 client_mac 00-00-00-00-00-01 ports all
Command: config filter dhcp_server add permit server_ip 10.1.1.1
client_mac 00-0
0-00-00-00-01 ports all
Success!
DES-1210-28/ME:5#
show filter dhcp_server
Purpose Used to display current DHCP server/client filter list created on the
switch.
Syntax
show filter dhcp_server
Description
The show filter dhcp_server command is used to display DHCP
server/client filter list created on the switch.
Parameters None.
Restrictions None.
Example usage:
To display the DHCP server filter list created on the switch:
DES-1210-28/ME:5# show filter dhcp_server
Command: show filter dhcp_server
IP Address MAC Address Ports
--------------- ----------------- ------------------------------
10.1.1.1 00-00-00-00-00-01 1-28
Total Entries: 1
Success!
DES-1210-28/ME:5#
Page 55
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
43
config dhcp_server screening ports
Purpose To configure a DHCP server screening from the DHCP Relay server
list.
Syntax
config dhcp_server screening ports <portlist> state [enable |
disable]
Description
The config dhcp_server screening ports command configures the
ports of DHCP servers screening on the Switch.
Parameters
<portlist> − Specifies a port or a range of ports to be configured.
state [enable | disable] − Enable/Disable the DHCP server
screening for the specified ports.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To configure the DHCP server screening of port 1~5 on the Switch:
DES-1210-28/ME:5# config dhcp_server screening ports 1-5 state enable
Command: config dhcp_server screening ports 1-5 state enable
Success.
DES-1210-28/ME:5#
show dhcp_server screening
Purpose To
display the DHCP server screening on the Switch
.
Syntax
show dhcp_server screening
Description
The show dhcp_server screening command displays the DHCP
server screening on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display DHCP server screening settings:
DES-1210-28/ME:5# show dhcp_server screening
Command: show dhcp_server screening
DHCP server screening :
Port Admin state
---- ----------1 disabled
2 disabled
3 disabled
4 disabled
5 disabled
6 disabled
7 disabled
8 disabled
9 disabled
Page 56
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
44
10 disabled
11 disabled
12 disabled
13 disabled
Page 57
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
45
12
1212
12
IP-MAC-PORT BINDING COMMANDS
The IP network layer uses a four-byte address. The Ethernet link layer uses a six-byte MAC address.
Binding these two address types together allows the transmission of data between the layers. The
primary purpose of IP-MAC-port binding is to restrict the access to a switch to a number of authorized
users. Only the authorized client can access the Switch’s port by checking the pair of IP-MAC addresses
with the pre-configured database. If an unauthorized user tries to access an IP-MAC-port binding
enabled port, the system will block the access by dropping its packet. The maximum number of IP-MACport binding entries is dependant on chip capability (e.g. the ARP table size) and storage size of the
device. For the Switch, the maximum value for the IP-MAC-port binding ARP mode is 500. The creation
of authorized users can be manually configured by CLI or Web. The function is port-based, meaning a
user can enable or disable the function on the individual port.
The IP-MAC-Port Binding commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table:
Command Parameter
create address_binding
ip_mac ipaddress
<ipaddr> mac_address <macaddr> ports <port 1-28>
config address_binding
ip_mac ports
[<portlist> | all] {state [disable | enable] | ip_inspection [disable | enable] |
arp_inspection [loose | strict]}
config address_binding
auto_scan
from_ip <ipaddr> to_ip <ipaddr>
delete address_binding
[ip_mac [ipaddress <ipaddr> mac_address <macaddr> | all] | blocked [all |
vlan_name <vlan_name> mac_address <macaddr> port <port 1-28>]]
show address_binding
{[ip_mac [all | {ipaddress <ipaddr> | mac_address <macaddr>}] | blocked [all |
vlan_name <vlan_name> mac_address <macaddr> port <port 1-28>] | ports]}
show address_binding
auto_scan list
enable
address_binding
dhcp_snoop
ports [<portlist> | all]
disable
address_binding
dhcp_snoop
ports [<portlist> | all]
Each command is listed in detail, as follows:
create address_binding ip_mac ipaddress
Purpose Used to create an IP-MAC-port binding entry.
Syntax
create address_binding ip_mac ipaddress <ipaddr>
mac_address <macaddr> ports <port 1-28>
Description
The create address_binding ip_mac ipaddress command is used to
create an IP-MAC-port binding entry.
Parameters
<ipaddr> – The IP address of the device where the IP-MAC-port
binding is made.
Page 58
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
46
<macaddr> – The MAC address of the device where the IP-MACport binding is made.
<port 1-28> – Specifies a port to be configured for address binding.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To create address binding on the Switch:
DES-1210-28/ME:5# create address_binding ip_mac ipaddress 10.0.0.21
mac_address 00-00-00-00-01-02 ports 3
Command: create address_binding ip_mac ipaddress 10.0.0.21
mac_address 00-00-00-00-01-02 ports 3
Success.
DES-1210-28/ME:5#
config address_binding ip_mac ports
Purpose Used to configure an IP-MAC-port binding state to enable or disable
for specified ports.
Syntax
config address_binding ip_mac ports [<portlist> | all] {state
[disable | enable] | ip_inspection [disable | enable] |
arp_inspection [loose | strict]}
Description
The config address_binding ip_mac ports command is used to
configure the IP-MAC-port binding state to enable or disable for
specified ports.
Parameters
<portlist> − Specifies a port or range of ports.
all – Specifies all ports on the switch.
[enable | disable] – Enables or disables the specified range of ports
for state and IP-inspection.
arp_inspection [loose | strict] – Specifies to check the ARP
inspection to be loose or stict for the specified ports.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To configure address binding on the Switch:
DES-1210-28/ME:5# config address_binding ip_mac ports 3 state disable
arp_inspection loose ip_inspection disable
Command: config address_binding ip_mac ports 3 state disable
arp_inspection loose ip_inspection disable
Success.
DES-1210-28/ME:5#
config address_binding auto_scan
Purpose Used to configure an IP-MAC-port binding auto scan for specified IP
addresses.
Syntax
config address_binding auto_scan from_ip <ipaddr> to_ip
<ipaddr>
Page 59
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
47
Description
The config address_binding auto_scan command is used to
configure the IP-MAC-port binding auto scan for specified IP
addresses.
Parameters
<ipaddr> − Specifies a range of IP addresses for address binding
auto scan on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To configure address binding auto scan on the Switch:
DES-1210-28/ME:5# config address_binding auto_scan from_ip 10.0.0.10
to_ip 10.0.0.12
Command: config address_binding auto_scan from_ip 10.0.0.10 to_ip
10.0.0.12
Success.
DES-1210-28/ME:5#
delete address_binding
Purpose Used to delete IP-MAC-port binding entries.
Syntax
delete address_binding [ip_mac [ipaddress <ipaddr>
mac_address <macaddr> | all] | blocked [all | vlan_name
<vlan_name> mac_address <macaddr> port <port 1-28>]]
Description
The delete address_binding command is used to delete IP-MACport binding entries. Two different kinds of information can be
deleted.
ip_mac – Individual address binding entries can be deleted by
entering the physical and IP addresses of the device. Toggling to all
will delete all the address binding entries.
blocked – Blocked address binding entries (bindings between VLAN
names and MAC addresses) can be deleted by entering the VLAN
name and the physical address of the device. To delete all the
blocked address binding entries, toggle all.
Parameters
<ipaddr> – The IP address of the device where the IP-MAC-port
binding is made.
<macaddr> – The MAC address of the device where the IP-MACport binding is made.
vlan_name <string 20> – The VLAN name of the VLAN that is bound
to a MAC address in order to block a specific device on a known
VLAN.
all – For IP-MAC-port binding all specifies all the IP-MAC-port
binding entries; for blocked address binding entries all specifies all
the blocked VLANs and their bound physical sddresses.
<port 1-28> – Specifies a port to be deleted for address binding.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To delete all address binding entries on the Switch:
DES-1210-28/ME:5# delete address_binding ip_mac all
Command: delete address_binding ip_mac all
Page 60
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
48
Success.
DES-1210-28/ME:5#
show address_binding
Purpose Used to display IP-MAC-port binding entries.
Syntax
show address_binding {[ip_mac [all | {ipaddress <ipaddr> |
mac_address <macaddr>}] | blocked [all | vlan_name
<vlan_name> mac_address <macaddr> port <port 1-28>] |
ports]}
Description This command is used to display IP-MAC-port binding entries. Four
different kinds of information can be viewed.
ip_mac – Address binding entries can be viewed by entering the
physical and IP addresses of the device.
blocked – Blocked address binding entries (bindings between VLAN
names and MAC addresses) can be viewed by entering the VLAN
name and the physical address of the device.
ports – The number of enabled ports on the device.
Parameters
ip_mac – The database the user creates for address binding.
all – For IP MAC binding all specifies all the IP-MAC-port binding
entries; for blocked address binding entries all specifies all the
blocked VLANs and their bound physical addresses.
blocked – The address database that the system auto learns and
blocks.
<ipaddr> – The IP address of the device where the IP-MAC-port
binding is made.
<macaddr> – The MAC address of the device where the IP-MACport binding is made.
vlan_name <string 20> – The VLAN name of the VLAN that is bound
to a MAC address in order to block a specific device on a known
VLAN.
port <port 1-28> – Specifies a port to be displayed for the address
binding on the Switch.
Restrictions None.
Example usage:
To display address binding entries on the Switch:
DES-1210-28/ME:5# show address_binding ip_mac all
Command: show address_binding ip_mac all
IP Address MAC Address Port
--------------- -------------------- ----
10.0.0.21 00-00-00-00-01-02 3
DES-1210-28/ME:5#
Page 61
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
49
show address_binding auto_scan list
Purpose Used to display IP-MAC-port binding entries.
Syntax
show address_binding auto_scan list
Description This command is used to display auto scan list of address binding
on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display the auto scan list of address binding on the Switch:
DES-1210-28/ME:5# show address_binding auto_scan list
Command: show address_binding auto_scan list
VLAN IP Address MAC Address Port Bound
---- --------------- ----------------- ---- -----
DES-1210-28/ME:5#
enable address_binding dhcp_snoop
Purpose Used to enable IP-MAC-port binding DHCP Snooping.
Syntax
enable address_binding dhcp_snoop ports [<portlist> | all]
Description This command is used to enable IP-MAC-port binding DHCP
snooping entries.
Parameters
[<portlist> | all] – Specifies a port, a range of ports or all ports to be
enabled of the address binding DHCP snooping on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To enable the DHCP snooping of address binding for port 3~5 on the Switch:
DES-1210-28/ME:5# enable address_binding dhcp_snoop ports 3-5
Command: enable address_binding dhcp_snoop ports 3-5
Success.
DES-1210-28/ME:5#
disable address_binding dhcp_snoop
Purpose Used to disable IP-MAC-port binding DHCP Snooping.
Syntax
disable address_binding dhcp_snoop ports [<portlist> | all]
Description This command is used to disable IP-MAC-port binding DHCP
snooping entries.
Parameters
[<portlist> | all] – Specifies a port, a range of ports or all ports to be
enabled of the address binding DHCP snooping on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Page 62
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
50
Example usage:
To disable the DHCP snooping of address binding for port 3~5 on the Switch:
DES-1210-28/ME:5# disable address_binding dhcp_snoop ports 4
Command: disable address_binding dhcp_snoop ports 4
Success.
DES-1210-28/ME:5#
Page 63
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
51
13
1313
13
NETWORK MANAGEMENT (SNMP) COMMANDS
The Switch supports the Simple Network Management Protocol (SNMP) versions 1, 2c, and 3. Users can
specify which version of the SNMP users want to use to monitor and control the Switch. The three
versions of SNMP vary in the level of security provided between the management station and the
network device. The following table lists the security features of the three SNMP versions:
SNMP Version Authentication Method Description
v1 Community String Community String is used for authentication - NoAuthNoPriv
v2c Community String Community String is used for authentication - NoAuthNoPriv
v3 Username Username is used for authentication – NoAuthNoPriv
v3 MD5 or SHA Authentication is based on the HMAC-MD5 or HMAC-SHA
algorithms – AuthNoPriv
v3 MD5 DES or SHA DES Authentication is based on the HMAC-MD5 or HMAC-SHA
algorithms – AuthPriv. DES 56-bit encryption is added based
on the CBC-DES(DES-56) standard
The Network Management commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
create snmp user
<username 32> <groupname 32> [v1 | v2c | v3 [MD5 <auth_password 32> |
SHA <auth_password 32> | none ] [DES <priv_password 32> | none]
delete snmp user
<username 32> [v1 | v2c | v3]
show snmp user
create snmp view
<view_name 32> <oid 32> <oid_mask 32 view_type [included | excluded]
delete snmp view
<view_name 32> <oid 32>
show snmp view
{<view_name 32>}
create snmp community <community_string 32> <username 32>
delete snmp community <community_string 32>
show snmp community {<community_string 32>}
config snmp engineID
<snmp_engineID 64>
show snmp engineID
create snmp group
<groupname 32> [v1 | v2c | v3 [noauth_nopriv | auth_nopriv |
auth_priv]{notify_view <view_name 32>}] {read_view <view_name 32> |
write_view <view_name 32>}
delete snmp group
<groupname 32> [v1 | v2c | v3] [auth_nopriv | auth_priv | noauth_priv]
show snmp global state
show snmp groups
Page 64
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
52
Command Parameter
create snmp host
<ipaddr> [v1 <username 32> | v2c <username 32> | v3 [noauth_nopriv |
auth_nopriv | auth_priv] <username 32>]
delete snmp host
<ipaddr>
show snmp host
{<ipaddr>}
enable trusted_host
disable trusted_host
create trusted_host
<ipaddr>{network <network_address>} {application [telnet | ssh | snmp | http |
https | ping | all}
show trusted_host
delete trusted_host
[<ipaddr> | all | network <network_address>]
enable snmp traps
disable snmp traps
enable snmp
authenticate trap
disable snmp
authenticate trap
show snmp traps
config syslocation <string 20>
config sysname <string 20>
enable snmp
disable snmp
enable snmp
DHCP_screening traps
diable snmp
DHCP_screening traps
enable snmp
IMPB_violation traps
disable snmp
IMPB_violation traps
enable snmp
fiber_port_link traps
disable snmp
fiber_port_link traps
enable snmp
firmware_upgrade_state
traps
disable snmp
firmware_upgrade_state
traps
enable snmp LBD traps
Page 65
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
53
Command Parameter
disable snmp LBD traps
enable snmp
port_security_violation
traps
disable snmp
port_security_violation
traps
enable snmp
rstpport_state_change
traps
disable snmp
rstpport_state_change
traps
enable snmp
system_device_bootup
traps
disable snmp
system_device_bootup
traps
enable snmp
twistedpair_port_link
traps
disable snmp
twistedpair_port_link
traps
enable snmp
duplicate_IP_detected
traps
disable snmp
duplicate_IP_detected
traps
Each command is listed in detail, as follows:
create snmp user
Purpose To create a new SNMP user and add the user to an SNMP group.
Syntax
create snmp user <username 32> <groupname 32> [v1 | v2c | v3
[MD5 <auth_password 32> | SHA <auth_password 32> | none ]
[DES <priv_password 32> | none]]
Description
The create snmp user command creates a new SNMP user and
adds the user to an existing SNMP group.
Parameters
<username 32> − The new SNMP username, up to 32 alphanumeric
characters.
<groupname 32> − The SNMP groupname the new SNMP user is
associated with, up to 32 alphanumeric characters.
auth - The user may also choose the type of authentication
Page 66
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
54
algorithms used to authenticate the snmp user. The choices are:
• MD5 − Specifies that the HMAC-MD5-96 authentication
level to be used. md5 may be utilized by entering one of the
following:
• <auth password 32> - A string of between 1 and 32
alphanumeric characters used to authorize the agent to
receive packets for the host.
• SHA − Specifies that the HMAC-SHA-96 authentication level
will be used.
• <priv_password 32> - A string of between 1 and 32
alphanumeric characters used to authorize the agent to
receive packets for the host.
• DES − Specifies that the DES authentication level will be
used.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To create an SNMP user on the Switch:
DES-1210-28/ME:5# create snmp user dlink SW22 v3 MD5 1234 DES jklj22
Command: create snmp user dlink SW22 v3 MD5 1234 DES jklj22
Success!
DES-1210-28/ME:5#
delete snmp user
Purpose To remove an SNMP user from an SNMP group and also to delete
the associated SNMP group.
Syntax
delete snmp user <username 32> [v1 | v2c | v3]
Description
The delete snmp user command removes an SNMP user from its
SNMP group and then deletes the associated SNMP group.
Parameters
<username 32> − A string of up to 32 alphanumeric characters that
identifies the SNMP user to be deleted.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To delete a previously created SNMP user on the Switch:
DES-1210-28/ME:5# delete snmp user dlink v3
Command: delete snmp user dlink v3
Success!
show snmp user
Purpose To display information about each SNMP username in the SNMP
group username table.
Page 67
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
55
Syntax
show snmp user
Description
The show snmp user command displays information about each
SNMP username in the SNMP group username table.
Parameters None.
Restrictions None.
Example usage:
To display the SNMP users currently configured on the Switch:
DES-1210-28/ME:5# show snmp user
Command: show snmp user
Username Group Name SNMP Version Auth-Protocol PrivProtocol
-------- ------------ ------------ ---------------- ----------------
ReadOnly ReadOnly V1 None None
ReadOnly ReadOnly V2 None None
ReadWrite ReadWrite V1 None None
ReadWrite ReadWrite V2 None None
Total Entries: 4
DES-1210-28/ME:5#
create snmp view
Purpose To assign views to community strings to limit which MIB objects an
SNMP manager can access.
Syntax
create snmp view <view_name 32> <oid 32> <oid_mask 32
view_type [included | excluded]
Description
The create snmp view command assigns views to community
strings to limit which MIB objects an SNMP manager can access.
Parameters
<view_name 32> − A string of up to 30 alphanumeric characters that
identifies the SNMP view to be created.
<oid 32> − The object ID that identifies an object tree (MIB tree) to
be included or excluded from access by an SNMP manager.
<oid_mask 32> − The object ID mask that identifies an object tree
(MIB tree) to be included or excluded from access by an SNMP
manager.
included − Includes this object in the list of objects that an SNMP
manager can access.
excluded − Excludes this object from the list of objects that an
SNMP manager can access.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To create an SNMP view:
DES-1210-28/ME:5# create snmp view dlink 1.3.6 1.1.1 view_type excluded
Command: create snmp view dlink 1.3.6 1.1.1 view_type excluded
Page 68
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
56
Success!
DES-1210-28/ME:5#
delete snmp view
Purpose To remove an SNMP view entry previously created on the Switch.
Syntax
delete snmp view <view_name 32> <oid 32>
Description
The delete snmp view command removes an SNMP view
previously created on the Switch.
Parameters
<view_name 32> − A string of up to 32 alphanumeric characters that
identifies the SNMP view to be deleted.
<oid 32> − The object ID that identifies an object tree (MIB tree) that
is deleted from the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To delete a previously configured SNMP view from the Switch:
DES-1210-28/ME:5# delete snmp view dlink 1.3.6
Command: delete snmp view dlink 1.3.6
Success.
DES-1210-28/ME:5#
show snmp view
Purpose To display an SNMP view previously created on the Switch.
Syntax
show snmp view {<view_name 32>}
Description
The show snmp view command displays an SNMP view previously
created on the Switch.
Parameters
<view_name 32> − A string of up to 30 alphanumeric characters that
identifies the SNMP view to be displayed.
Restrictions None.
Example usage:
To display SNMP view configuration:
DES-1210-28/ME:5# show snmp view
Command: show snmp view
SNMP View Table Configuration
View Name Subtree OID OID Mask View Type
------------ ---------------------- ---------------------- --------dlink 1.2.3.4 1.1.1.1 Excluded
ReadWrite 1 1 Included
Page 69
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
57
Total Entries: 2
DES-1210-28/ME:5#
create snmp community
Purpose To create an SNMP community string to define the relationship
between the SNMP manager and an SNMP agent.
Syntax
create snmp community <community_string 32> <username
32>
Description
The create snmp community command creates an SNMP
community string and assigns access-limiting characteristics to this
community string. The community string acts like a password to
permit access to the agent on the Switch. One or more of the
following characteristics can be associated with the community
string:
An Access List of IP addresses of SNMP managers that are
permitted to use the community string to gain access to the Switch’s
SNMP agent.
An MIB view that defines the subset of all MIB objects to be
accessible to the SNMP community.
Read/write or read-only level permission for the MIB objects
accessible to the SNMP community.
Parameters
<community_string 32> − A string of up to 32 alphanumeric
characters that is used to identify members of an SNMP community.
This string is used like a password to give remote SNMP managers
access to MIB objects in the Switch’s SNMP agent.
<username 32> − A string of up to 32 alphanumeric characters that
is used to identify the group of MIB objects that a remote SNMP
manager is allowed to access on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To create the SNMP community string ‘dlink:’
DES-1210-28/ME:5# create snmp community dlinkgroup dlink
Success.
DES-1210-28/ME:5#
delete snmp community
Purpose To remove a specific SNMP community string from the Switch.
Syntax
delete snmp community <community_string 32>
Description
The delete snmp community command removes a previously
defined SNMP community string from the Switch.
Parameters
<community_string 32> − A string of up to 32 alphanumeric
characters that is used to identify members of an SNMP community
to delete. This string is used like a password to give remote SNMP
managers access to MIB objects in the Switch’s SNMP agent.
Page 70
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
58
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To delete the SNMP community string ‘dlink’:
DES-1210-28/ME:5# delete snmp community dlink
Command: delete snmp community dlink
Success!
DES-1210-28/ME:5#
show snmp community
Purpose To display SNMP community strings configured on the Switch.
Syntax
show snmp community {<community_string 32>}
Description
The show snmp community command displays SNMP community
strings that are configured on the Switch.
Parameters
<community_string 32> − A string of up to 20 alphanumeric
characters that is used to identify members of an SNMP community.
This string is used like a password to give remote SNMP managers
access to MIB objects in the Switch’s SNMP agent.
Restrictions None.
Example usage:
To display the currently entered SNMP community strings:
DES-1210-28/ME:5# show snmp community
Command: show snmp community
SNMP Community Table
(Maximum Entries : 10)
Community Name User Name
------------------ -----------public ReadOnly
private ReadWrite
Total Entries: 2
DES-1210-28/ME:5#
config snmp engineID
Purpose To configure a name for the SNMP engine on the Switch.
Syntax
config snmp engineID <snmp_engineID 64>
Description
The config snmp engineID command configures a name for the
SNMP engine on the Switch.
Parameters
<snmp_engineID 64> − A string, of between 10 and 64
Page 71
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
59
alphanumeric characters, to be used to identify the SNMP engine on
the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To give the SNMP agent on the Switch:
DES-1210-28/ME:5# config snmp engineID 12345678900
Command: config snmp engineID 12345678900
Success!
DES-1210-28/ME:5#
show snmp engineID
Purpose To display the identification of the SNMP engine on the Switch.
Syntax
show snmp engineID
Description
The show snmp engineID command displays the identification of
the SNMP engine on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display the current name of the SNMP engine on the Switch:
DES-1210-28/ME:5# show snmp engineID
Command: show snmp engineID
Default SNMP Engine ID : 4445532d313231
SNMP Engine ID : 012345678900
DES-1210-28/ME:5#
create snmp group
Purpose To create a new SNMP group, or a table that maps SNMP users to
SNMP views.
Syntax
create snmp group <groupname 32> [v1 | v2c | v3
[noauth_nopriv | auth_nopriv | auth_priv]{notify_view
<view_name 32>}] {read_view <view_name 32> | write_view
<view_name 32>}
Description
The create snmp group command creates a new SNMP group, or
a table that maps SNMP users to SNMP views.
Parameters
<groupname 32> − A name of up to 30 alphanumeric characters that
identifies the SNMP group the new SNMP user is to be associated
with.
v1 – Specifies that SNMP version 1 is to be used. The Simple
Network Management Protocol (SNMP), version 1, is a network
management protocol that provides a means to monitor and control
Page 72
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
60
network devices.
v2c – Specifies that SNMP version 2c is to be used. The SNMP v2c
supports both centralized and distributed network management
strategies. It includes improvements in the Structure of Management
Information (SMI) and adds some security features.
v3 – Specifies that the SNMP version 3 is to be used. SNMP v3
provides secure access to devices through a combination of
authentication and encrypting packets over the network. SNMP v3
adds:
• Message integrity − Ensures that packets have not been
tampered with during transit.
• Authentication − Determines if an SNMP message is from a
valid source.
• Encryption − Scrambles the contents of messages to
prevent it from being viewed by an unauthorized source.
noauth_nopriv − Specifies that there is no authorization and no
encryption of packets sent between the Switch and a remote SNMP
manager.
auth_nopriv − Specifies that authorization is required, but there is no
encryption of packets sent between the Switch and a remote SNMP
manager.
auth_priv − Specifies that authorization is required, and that packets
sent between the Switch and a remote SNMP manger are
encrypted.
read_view – Specifies that the SNMP group being created can
request SNMP messages.
• <view_name 32> − A string of up to 32 objects that a remote
SNMP manager is allowed to access on the Switch.
write_view – Specifies that the SNMP group being created has write
privileges.
• <view_name 32 identifies the group of MIB objects that a
remote SNMP manager is allowed to access on the Switch.
notify_view − Specifies that the SNMP group being created can
receive SNMP trap messages generated by the Switch’s SNMP
agent.
• <view_name 32> − A string of up to 32 alphanumeric
characters that identifies the group of MIB objects that a
remote SNMP manager is allowed to access on the Switch.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To create an SNMP group named ‘sg1:’
DES-1210-28/ME:5# create snmp group sg1 v2c read_view sg1 write_view sg1
notify_view sg1
Command: create snmp group sg1 v2c read_view sg1 write_view sg1 notify_view
sg1
Success!
DES-1210-28/ME:5#
Page 73
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
61
delete snmp group
Purpose To remove an SNMP group from the Switch.
Syntax
delete snmp group <groupname 32> [v1 | v2c | v3 [auth_priv |
noauth_nopriv]]
Description
The delete snmp group command removes an SNMP group from
the Switch.
Parameters
<groupname 32> − A string of that identifies the SNMP group the
new SNMP user will be associated with. Up to 32 alphanumeric
characters.
Restrictions Only administrator or operate-level users can issue this command.
Example usage:
To delete the SNMP group named ‘sg1’:
DES-1210-28/ME:5# delete snmp group sg1 v3 auth_priv
Command: delete snmp group sg1 v3 auth_priv
Success!
DES-1210-28/ME:5#
show snmp global state
Purpose To display the global state of SNMP currently configured on the
Switch.
Syntax
show snmp global state
Description
The show snmp global state command displays the global state of
SNMP groups currently configured on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display the currently configured SNMP global state on the Switch:
DES-1210-28/ME:5# show snmp global state
Command: show snmp global state
SNMP Global State : Enable
DES-1210-28/ME:5#
show snmp groups
Purpose To display the group-names of SNMP groups currently configured
on the Switch. The security model, level, and status of each group
are also displayed.
Page 74
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
62
Syntax
show snmp groups
Description
The show snmp groups command displays the group-names of
SNMP groups currently configured on the Switch. The security
model, level, and status of each group are also displayed.
Parameters None.
Restrictions None.
Example usage:
To display the currently configured SNMP groups on the Switch:
DES-1210-28/ME:5# show snmp groups
Command: show snmp groups
SNMP Group Table
Group Name Read View Write View Notify View Security Model Security Level
------------------ -------------- ---------------- --------------- ---------------------- ----------------sg1 df df d v3 AuthPriv
ReadOnly ReadWrite --- ReadWrite v1 NoAuthNoPriv
ReadOnly ReadWrite --- ReadWrite v2c NoAuthNoPriv
ReadWrite ReadWrite ReadWrite ReadWrite v1 NoAuthNoPriv
ReadWrite ReadWrite ReadWrite ReadWrite v2c NoAuthNoPriv
Total Entries: 5
DES-1210-28/ME:5#
create snmp host
Purpose To create a recipient of SNMP traps generated by the Switch’s
SNMP agent.
Syntax
create snmp host <ipaddr> [v1 <username 32> | v2c <username
32> | v3 [noauth_nopriv | auth_nopriv | auth_priv] <username
32>]
Description
The create snmp host command creates a recipient of SNMP traps
generated by the Switch’s SNMP agent.
Parameters
<ipaddr> − The IP address of the remote management station to
serve as the SNMP host for the Switch.
v1 – Specifies that SNMP version 1 is to be used. The Simple
Network Management Protocol (SNMP), version 1, is a network
management protocol that provides a means to monitor and control
network devices.
v2c – Specifies that SNMP version 2c is to be used. The SNMP v2c
supports both centralized and distributed network management
strategies. It includes improvements in the Structure of Management
Information (SMI) and adds some security features.
v3 – Specifies that the SNMP version 3 is to be used. SNMP v3
provides secure access to devices through a combination of
authentication and encrypting packets over the network. SNMP v3
adds:
• Message integrity − ensures that packets have not been
Page 75
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
63
tampered with during transit.
• Authentication − determines if an SNMP message is from a
valid source.
• Encryption − scrambles the contents of messages to prevent
it being viewed by an unauthorized source.
<username 32> − A string of up to 32 alphanumeric characters that
identifies user name of an SNMP community. This string is used like
a password to give remote SNMP managers access to MIB objects
in the Switch’s SNMP agent.
noauth_nopriv − Specifies that there is no authorization and no
encryption of packets sent between the Switch and a remote SNMP
manager.
auth_nopriv − Specifies that authorization is required, but there is no
encryption of packets sent between the Switch and a remote SNMP
manager.
auth_priv − Specifies that authorization is required, and that packets
sent between the Switch and a remote SNMP manger are
encrypted.
Restrictions Only Administrator and oper-level users can issue this command
Example usage:
To create an SNMP host to receive SNMP messages:
DES-1210-28/ME:5# create snmp host 10.90.90.22 v3 noauth_nopriv
dlink
Command: create snmp host 10.90.90.22 v3 noauth_nopriv dlink
Success!
DES-1210-28/ME:5#
delete snmp host
Purpose To remove a recipient of SNMP traps generated by the Switch’s
SNMP agent.
Syntax
delete snmp host <ipaddr>
Description
The delete snmp host command deletes a recipient of SNMP traps
generated by the Switch’s SNMP agent.
Parameters
<ipaddr> − The IP address of a remote SNMP manager that
receives SNMP traps generated by the Switch’s SNMP agent.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To delete an SNMP host entry:
DES-1210-28/ME:5# delete snmp host 10.90.90.22
Command: delete snmp host 10.90.90.22
Success!
DES-1210-28/ME:5#
Page 76
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
64
show snmp host
Purpose To display the recipient of SNMP traps generated by the Switch’s
SNMP agent.
Syntax
show snmp host {<ipaddr>}
Description
The show snmp host command is used to display the IP addresses
and configuration information of remote SNMP managers that are
designated as recipients of SNMP traps generated by the Switch’s
SNMP agent.
Parameters
<ipaddr> − The IP address of a remote SNMP manager that
receives SNMP traps generated by the Switch’s SNMP agent.
Restrictions None.
Example usage:
To display the currently configured SNMP hosts on the Switch:
DES-1210-28/ME:5# show snmp host
Command: show snmp host
SNMP Host Table
(Maximum Entries : 10)
Host IP Address SNMP Version Community Name/SNMPv3 User Name
------------------------ --------------------- -------------------------------------------------------
10.90.90.22 V3-NoAuthNoPriv dlink
Total Entries : 1
DES-1210-28/ME:5#
enable trusted_host
Purpose To enable the trusted host.
Syntax
enable trusted_host
Description
The enable trusted_host command enables the trusted host
feature.
Parameters None.
Restrictions Only administrator or operator level users can issue this command.
Example usage:
To enable the trusted host on the Swtich:
DES-1210-28/ME:5# enable trusted_host
Command: enable trusted_host
Success!
DES-1210-28/ME:5#
Page 77
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
65
disable trusted_host
Purpose To enable the trusted host.
Syntax
disable trusted_host
Description
The disable trusted_host command disables the trusted host
feature.
Parameters None.
Restrictions Only administrator or operator level users can issue this command.
Example usage:
To disable the trusted host on the Swtich:
DES-1210-28/ME:5# disable trusted_host
Command: disable trusted_host
Success!
DES-1210-28/ME:5#
create trusted_host
Purpose To create a trusted host.
Syntax
create trusted_host <ipaddr>{network <network_address>}
Description
The create trusted_host command creates a trusted host. The
Switch allows specifying up to 30 IP addresses that are allowed to
manage the Switch via in-band based management software. These
IP addresses must be members of the Management VLAN. If no IP
addresses are specified, then there is nothing to prevent any IP
address from accessing the Switch, provided the user knows the
Username and Password.
Parameters
<ipaddr> − The IP address of the trusted host to be created.
<network_address> − The subnet mask of the trusted host to be
created. This parameter is optional. If not specified, the default
subnet mask is 255.255.255.0.
Restrictions Only administrator or operator level users can issue this command.
Example usage:
To create the trusted host:
DES-1210-28/ME:5# create trusted_host 10.90.90.91
Command: create trusted_host 10.90.90.91
Success.
DES-1210-28/ME:5#
show trusted_host
Purpose To display a list of trusted hosts entered on the Switch using the
create trusted_host command above.
Page 78
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
66
Syntax
show trusted_host
Description
The show trusted_host command displays a list of trusted hosts
entered on the Switch using the create trusted_host command
above.
Parameters
None.
Restrictions None.
Example usage:
To display the list of trusted hosts:
DES-1210-28/ME:5# show trusted_host
Command: show trusted_host
Trusted Host Status : Enable
Management Stations
IP Address Subnet Mask
----------------- ---------------
10.90.90.91 255.255.255.255
10.90.90.92 255.255.255.255
Total Entries: 2
DES-1210-28/ME:5#
delete trusted_host
Purpose
To delete a trusted host entry made using the create trusted_host
command above.
Syntax
delete trusted_host [<ipaddr> | all | network
<network_address>]
Description
The delete trusted_host command deletes a trusted host entry
made using the create trusted_host command above.
Parameters
<ipaddr> − The IP address of the trusted host.
all − The all IP address of the trusted host.
network <network_address> − The subnet mask of the trusted host
to be deleted. This parameter is optional.
Restrictions Only administrator or operator level users can issue this command.
Example usage:
To delete a trusted host with an IP address 10.90.90.91:
DES-1210-28/ME:5# delete trusted_host 10.90.90.91
Command: delete trusted_host 10.90.90.91
Success.
DES-1210-28/ME:5#
Page 79
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
67
enable snmp traps
Purpose To enable SNMP trap support.
Syntax
enable snmp traps
Description
The enable snmp traps command enables SNMP trap support on
the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To enable SNMP trap support on the Switch:
DES-1210-28/ME:5# enable snmp traps
Command: enable snmp traps
Success!
DES-1210-28/ME:5#
disable snmp traps
Purpose To disable SNMP trap support on the Switch.
Syntax
disable snmp traps
Description
The disable snmp traps command disables SNMP trap support on
the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To prevent SNMP traps from being sent from the Switch:
DES-1210-28/ME:5# disable snmp traps
Command: disable snmp traps
Success!
DES-1210-28/ME:5#
enable snmp authenticate trap
Purpose To enable SNMP authentication trap support.
Syntax
enable snmp authenticate trap
Description
The enable snmp authenticate trap command enables SNMP
authentication trap support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To turn on SNMP authentication trap support:
Page 80
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
68
DES-1210-28/ME:5# enable snmp authenticate traps
Command: enable snmp authenticate traps
Success!
DES-1210-28/ME:5#
disable snmp authenticate trap
Purpose To disable SNMP authentication trap support.
Syntax
disable snmp authenticate trap
Description
The disable snmp authenticate trap command disables SNMP
authentication trap support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable the SNMP authentication trap support:
DES-1210-28/ME:5# disable snmp authenticate traps
Command: disable snmp authenticate traps
Success!
DES-1210-28/ME:5#
show snmp traps
Purpose To display SNMP trap support status on the Switch.
Syntax
show snmp traps
Description
The show snmp traps command displays the SNMP trap support
status currently configured on the Switch.
Parameters None.
Restrictions None.
Example usage:
To view the current SNMP trap support:
DES-1210-28/ME:5# show snmp traps
Command: show snmp traps
SNMP Traps : Disable
SNMP Authentication Traps : Disable
System Device Bootup : Disable
Fiber Port Link Up / Link Down : Disable
Twisted Pair Port Link Up / Link Down : Disable
RSTP Port State Change : Disable
Firmware Upgrade State : Disable
Port Security State : Disable
Page 81
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
69
IMPBv2 State : Disable
Loopback detection State : Disable
DHCP server screen State : Disable
Gratutious ARP State : Disable
DES-1210-28/ME:5#
config syslocation
Purpose To enter a description of the location of the Switch.
Syntax
config syslocation <string 20>
Description
The config syslocation command enters a description of the
location of the Switch. A maximum of 20 characters can be used.
Parameters
<string 20> - A maximum of 20 characters is allowed.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To configure the Switch location for ‘HQ5F’:
DES-1210-28/ME:5# config syslocation HQ5F
Command: config syslocation HQ5F
Success.
DES-1210-28/ME:5#
config sysname
Purpose To define the name for the Switch.
Syntax
config sysname <string 20>
Description
The config sysname command defines the name of the Switch.
Parameters
<string 20> - A maximum of 20 characters is allowed.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To configure the Switch name as ‘28ME’:
DES-1210-28/ME:5# config sysname 28ME
Command: config sysname 28ME
Success.
DES-1210-28/ME:5#
enable snmp
Purpose To enable SNMP support.
Syntax
enable snmp
Page 82
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
70
Description
The enable snmp command enables SNMP support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To enable SNMP support on the Switch:
DES-1210-28/ME:5# enable snmp
Command: enable snmp
Success!
DES-1210-28/ME:5#
disable snmp
Purpose To disable SNMP support.
Syntax
disable snmp
Description
The disable snmp command enables SNMP support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable SNMP support on the Switch:
DES-1210-28/ME:5# disable snmp
Command: disable snmp
Success!
DES-1210-28/ME:5#
enable snmp DHCP_ screening traps
Purpose To enable SNMP DHCP screening traps.
Syntax
enable snmp DHCP_screening traps
Description
The enable snmp DHCP_screening traps command enables
SNMP DHCP screening traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To enable SNMP DHCP screening traps support on the Switch:
DES-1210-28/ME:5# enable snmp DHCP_screening traps
Command: enable snmp DHCP_screening traps
Success!
Page 83
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
71
DES-1210-28/ME:5#
disable snmp DHCP_ screening traps
Purpose To disable SNMP DHCP screening traps.
Syntax
disable snmp DHCP_screening traps
Description
The disable snmp DHCP_screening traps command enables
SNMP DHCP screening traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable SNMP DHCP screening traps support on the Switch:
DES-1210-28/ME:5# disable snmp DHCP_screening traps
Command: disable snmp DHCP_screening traps
Success!
DES-1210-28/ME:5#
enable snmp IMPB_violation traps
Purpose To enable SNMP IMPB violation traps.
Syntax
enable snmp IMPB_violation traps
Description
The enable snmp IMPBv2 traps command enables SNMP IMPB
violation traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To enable SNMP IMPB violation traps support on the Switch:
DES-1210-28/ME:5# enable snmp IMPB_violation traps
Command: enable snmp IMPB_violation traps
Success!
DES-1210-28/ME:5#
disable snmp IMPB_violation traps
Purpose To disable SNMP IMPB violation traps.
Syntax
disable snmp IMPB_violation traps
Description
The disable snmp IMPB_violation traps command enables SNMP
IMPB violation traps support on the Switch.
Parameters None.
Page 84
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
72
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable SNMP IMPB violation traps support on the Switch:
DES-1210-28/ME:5# disable snmp IMPB_violation traps
Command: disable snmp IMPB_violation traps
Success!
DES-1210-28/ME:5#
enable snmp fiber_port_link traps
Purpose To enable SNMP fiber port link traps support on the Switch.
Syntax
enable snmp fiber_port_link traps
Description
The enable snmp fiber_port_link traps command enables SNMP
fiber port link traps support on the Switch. After enables the SNMP
fiber port link traps support, the Switch will send out a trap to the
SNMP manage host when the fiber port is link up or link down.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To enable SNMP fiber port link traps support on the Switch:
DES-1210-28/ME:5# enable snmp fiber_port_link traps
Command: enable snmp fiber_port_link traps
Success!
DES-1210-28/ME:5#
disable snmp fiber_port_link traps
Purpose To disable SNMP fiber port link traps.
Syntax
disable snmp fiber_port_link traps
Description
The disable snmp fiber_port_link traps command disables SNMP
fiber port link traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable SNMP fiber port link traps support on the Switch:
DES-1210-28/ME:5# disable snmp fiber_port_link traps
Command: disable snmp fiber_port_link traps
Page 85
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
73
Success!
DES-1210-28/ME:5#
enable snmp firmware_upgrade_state traps
Purpose To enable SNMP firmware upgrade state traps.
Syntax
enable snmp firmware_upgrade_state traps
Description
The enable snmp firmware_upgrade_state traps command
enables SNMP firmware upgrade state traps support on the Switch.
After enables the SNMP firmware upgrade state traps support, the
Switch will send out a trap to the SNMP manage host when the
firmware upgrade is succeed or fail.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable SNMP firmware upgrade state traps support on the Switch:
DES-1210-28/ME:5# enable snmp firmware_upgrade_state traps
Command: enable snmp firmware_upgrade_state traps
Success!
DES-1210-28/ME:5#
disable snmp firmware_upgrade_state traps
Purpose To disable SNMP firmware upgrade state traps.
Syntax
disable snmp firmware_upgrade_state traps
Description
The disable snmp firmware_upgrade_state traps command
disables SNMP firmware upgrade state traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable SNMP firmware upgrade state traps support on the Switch:
DES-1210-28/ME:5# disable snmp firmware_upgrade_state traps
Command disable enable snmp firmware_upgrade_state traps
Success!
DES-1210-28/ME:5#
enable snmp LBD traps
Purpose To enable SNMP LBD traps.
Page 86
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
74
Syntax
enable snmp LBD traps
Description
The enable snmp LBD traps command enables SNMP LBD traps
support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable SNMP LBD traps support on the Switch:
DES-1210-28/ME:5# enable snmp LBD traps
Command: enable snmp LBD traps
Success!
DES-1210-28/ME:5#
disable snmp LBD traps
Purpose To disable SNMP LBD traps.
Syntax
disable snmp LBD traps
Description
The disable snmp LBD traps command disables SNMP LBD traps
support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
To disable SNMP LBD traps support on the Switch:
DES-1210-28/ME:5# disable snmp LBD traps
Command: disable snmp LBD traps
Success!
DES-1210-28/ME:5#
enable snmp port_security_violation traps
Purpose To enable SNMP port security violation traps.
Syntax
enable snmp port_security_violation traps
Description
The enable snmp port_security_violation traps command
enables SNMP port security violation traps on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable SNMP port security violation traps support on the Switch:
DES-1210-28/ME:5# enable snmp port_security_violation traps
Page 87
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
75
Command: enable snmp port_security_violation traps
Success!
DES-1210-28/ME:5#
disable snmp port_security_violation traps
Purpose To disable SNMP port security violation traps.
Syntax
disable snmp port_security_violation traps
Description
The disable snmp port_security_violation traps command
disables SNMP port security violation traps on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable SNMP port security violation traps support on the Switch:
DES-1210-28/ME:5# disable snmp port_security_violation traps
Command: disable snmp port_security_violation traps
Success!
DES-1210-28/ME:5#
enable snmp rstpport_state_change traps
Purpose To enable SNMP rstp port state change traps support on the Switch.
Syntax
enable snmp rstpport_state_change traps
Description
The enable snmp rstpport_state_change traps command enables
SNMP rstp port state change traps support on the Switch. After
enables the SNMP RSTP port state change traps support, the
Switch will send out a trap when the state of RSTP port is changed.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable SNMP RSTP port state change traps support on the Switch:
DES-1210-28/ME:5# enable snmp rstpport_state_change traps
Command: enable snmp rstpport_state_change traps
Success!
DES-1210-28/ME:5#
Page 88
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
76
disable snmp rstpport_state_change traps
Purpose To disable SNMP RSTP port state change traps.
Syntax
disable snmp rstpport_state_change traps
Description
The disable snmp rstpport_state_change traps command
disables SNMP RSTP port state change traps on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable SNMP RSTP port state change traps support on the Switch:
DES-1210-28/ME:5# disable snmp rstpport_state_change traps
Command: disable snmp rstpport_state_change traps
Success!
DES-1210-28/ME:5#
enable snmp system_device_bootup traps
Purpose To enable SNMP system device bootup traps support on the Switch.
Syntax
enable snmp system_device_bootup traps
Description
The enable snmp system_device_bootup traps command
enables SNMP system device bootup traps support on the Switch.
After enables the SNMP system device bootup traps support, the
Switch will send out a trap to the SNMP manage host when the
device is power on.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable the SNMP system device bootup traps on the Switch:
DES-1210-28/ME:5# enable snmp system_device_bootup traps
Command: enable snmp system_device_bootup traps
Success!
DES-1210-28/ME:5#
disable snmp system_device_bootup traps
Purpose To disable SNMP system device bootup traps support on the Switch.
Syntax
disable snmp system_device_bootup traps
Description
The disable snmp system_device_bootup traps command
disables SNMP system device bootup traps support on the Switch.
Page 89
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
77
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable the SNMP system device bootup traps on the Switch:
DES-1210-28/ME:5# disable snmp system_device_bootup traps
Command: disable snmp system_device_bootup traps
Success!
DES-1210-28/ME:5#
enable snmp twistedpair_port_link traps
Purpose To enable SNMP twisted pair ports link traps support on the Switch.
Syntax
enable snmp twistedpair_port_link traps
Description
The enable snmp twistedpair_port_link traps command enables
SNMP twisted pair ports link traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable the SNMP twisted pair ports link traps on the Switch:
DES-1210-28/ME:5# enable snmp twistedpair_port_link traps
Command: enable snmp twistedpair_port_link traps
Success!
DES-1210-28/ME:5#
disable snmp twistedpair_port_link traps
Purpose To disable SNMP twisted pair ports link traps support on the Switch.
Syntax
disable snmp twistedpair_port_link traps
Description
The disable snmp twistedpair_port_link traps command enables
SNMP twisted pair ports link traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable the SNMP twisted pair ports link traps on the Switch:
DES-1210-28/ME:5# disable snmp twistedpair_port_link traps
Command: disable snmp twistedpair_port_link traps
Page 90
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
78
Success!
DES-1210-28/ME:5#
enable snmp duplicate_IP_detected traps
Purpose To enable SNMP duplicate IP detected traps support on the Switch.
Syntax
enable snmp duplicate_IP_detected traps
Description
The enable snmp duplicate_IP_detected traps command enables
SNMP duplicate IP detected traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To enable the SNMP duplicate_IP_detected traps on the Switch:
DES-1210-28/ME:5# enable snmp duplicate_IP_detected traps
Command: enable snmp duplicate_IP_detected traps
Success!
DES-1210-28/ME:5#
disable snmp duplicate_IP_detected traps
Purpose To disable SNMP duplicate IP detected traps support on the Switch.
Syntax
disable snmp duplicate_IP_detected traps
Description
The disable snmp duplicate_IP_detected traps command
disables SNMP duplicate IP detected traps support on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable the SNMP duplicate_IP_detected traps on the Switch:
DES-1210-28/ME:5# disable snmp duplicate_IP_detected traps
Command: disable snmp duplicate_IP_detected traps
Success!
DES-1210-28/ME:5#
Page 91
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
79
14
1414
14
DOWNLOAD/UPLOAD COMMANDS
The Download/Upload commands in the Command Line Interface (CLI) are listed (along with the
appropriate parameters) in the following table.
Command Parameter
download
[configuration <ipaddr> <path_filename 64> startup] | [firmware <ipaddr> <string
64>]
upload
[[firmware <ipaddr> <path_filename 64>] | [cfg_toTFTP <ipaddr> <path_filename
64> config_id <value 1-2>] | [log_toTFTP <ipaddr> <path_filename 64>]]
Each command is listed in detail, as follows:
download
Purpose To download and install a firmware, boot, or switch configuration file
from a TFTP server.
Syntax
download [configuration <ipaddr> <path_filename 64> startup] |
[firmware <ipaddr> <string 64>]
Description
The download command downloads a firmware, boot, or switch
configuration file from a TFTP server.
Parameters
configuration − Downloads a switch configuration file from a TFTP
server.
<ipaddr> − The IP address of the TFTP server.
<path_filename 64> − The DOS path and filename of the switch
configuration file, up to 64 characters, on the TFTP server. For
example, C:\31xx.had.
startup − Indicates the Configuration file is to be downloaded to the
startup config.
firmware − Downloads and installs firmware on the Switch from a
TFTP server.
<string 64> − The DOS path and filename of the firmware file, up to
64 characters, on the TFTP server. For example, C:\31xx.had.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To download a firmware file:
DES-1210-28/ME:5# download firmware 1.1.1.23 1\des_1210-28me.ros
Command: download firmware 1.1.1.23 1\des_1210-28me.ros
01–Jan–2000 01:19:48 %COPY–I–FILECPY: Files Copy – source URL tftp://1.1.1.23 /1\
des_1210-28me.ros destination URL Unit all flash://image
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
Page 92
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
80
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!01–Jan–2000 01:22:49 %COPY–W–TRAP:
The copy operation was completed successfully
!
3920460 bytes copied in 00:03:01 [hh:mm:ss]
DES-1210-28/ME:5#
To download a configuration file:
DES-1210-28/ME:5# download configuration 10.48.74.121 c:\cfg\setting.txt
Overwrite file [startup-config] ?[Yes/press any key for no]....
01-Jan-200003:19:46%COPY-I-FILECPY:FilesCopy-source URL tftp://10.48.74.121/1.txt
destination
URL flash://startup-config
Success.
Success.
.....01-Jan-2000 03:18:40 %COPY-N-TRAP: The copy operation was completed
successfully!
Copy: 267 bytes copied in 00:00:08 [hh:mm:ss]
DES-1210-28/ME:5#
upload
Purpose To upload the current switch settings to a TFTP server.
Syntax
upload [[firmware <ipaddr> <path_filename 64>] | [cfg_toTFTP
<ipaddr> <path_filename 64> config_id <value 1-2>] |
[log_toTFTP <ipaddr> <path_filename 64>]]
Description
The upload command uploads the Switch’s current settings to a
TFTP server.
Parameters
firmware − Specifies that the Switch’s current firmware are to be
uploaded to the TFTP server.
<ipaddr> − The IP address of the TFTP server. The TFTP server
must be on the same IP subnet as the Switch.
<path_filename 64> − The location of the Switch configuration file on
the TFTP server.
config_id <value 1-2> − Specifies the config id which to be
uploaded.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
DES-1210-28/ME:5# upload log_toTFTP 1.1.1.23 des-1210-28me.ros
Command: upload log_toTFTP 1.1.1.23 des-1210-28me.ros
01–Jan–2000 01:26:11 %COPY–I–FILECPY: Files Copy – source
URL running–config destination URL tftp://1.1.1.23/1\running–
Page 93
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
81
config
… ..01–Jan–2000 01:26:16 %COPY–W–TRAP: The copy operation
was completed success fully!
158 bytes copied in 00:00:05 [hh:mm:ss]
DES-1210-28/ME:5#
Page 94
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
82
15
1515
15
DHCP RELAY COMMANDS
The DHCP Relay commands in the Command Line Interface (CLI) are listed (along with the appropriate
parameters) in the following table.
Command Parameter
enable dhcp_relay
disable dhcp_relay
config dhcp_relay add
ipif system
<ipaddr>
config dhcp_relay
delete ipif system
<ipaddr>
config dhcp_relay hops <value 1-16>
config dhcp_relay
option_82
[check [enable | disable] | policy [drop | keep | replace] | remote_id [default |
user_define <string 32>] | state [enable | disable]]
show dhcp_relay {ipif}
enable
dhcp_local_relay
disable
dhcp_local_relay
config dhcp_local_relay
vlan
<vlan_name> | vlanid <vidlist>] state[enable | disable]
show dhcp_local_relay
Each command is listed in detail, as follows:
enable dhcp_relay
Purpose To enable DHCP Relay server on the Switch
Syntax
enable dhcp_relay
Description
The enable dhcp_relay command sets the DHCP Relay to be
globally enabled on the Switch and on all existing VLANs.
Parameters None.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To enable DCHP Relay on the Switch:
DES-1210-28/ME:5# enable dhcp_relay
Command: enable dhcp_relay
Success!
Page 95
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
83
DES-1210-28/ME:5#
disable dhcp_relay
Purpose To disable DHCP Relay server on the Switch
Syntax
disable dhcp_relay
Description
The disable dhcp_relay command sets the DHCP Relay to be
globally disabled on the Switch and on all existing VLANs.
Parameters None.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To disable DHCP Relay on the Switch:
DES-1210-28/ME:5# disable dhcp_relay
Command: disable dhcp_relay
Success!
DES-1210-28/ME:5#
config dhcp_relay add ipif system
Purpose
To define a DHCP server as a DHCP Relay server
Syntax
config dhcp_relay add ipif system <ipaddr>
Description
The config dhcp_relay add ipif system command adds DHCP
servers as DHCP Relay servers.
Parameters
<ipaddr> − The IP address of the DHCP server. Up to 4 servers can
be defined.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To add a DHCP server as a DHCP Relay server:
DES-1210-28/ME:5# config dhcp_relay add ipif System 10.6.150.49
Command: config dhcp_relay add ipif System 10.6.150.49
Success!
DES-1210-28/ME:5#
Page 96
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
84
config dhcp_relay delete ipif system
Purpose To delete a DHCP server from the DHCP Relay server list.
Syntax
config dhcp_relay delete ipif system <ipaddr>
Description
The config dhcp_relay delete ipif system command deletes a
DHCP servers defined as a DHCP Relay server.
Parameters
<ipaddr> − The IP address of the DHCP server.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To remove a DHCP server from the DHCP Relay server list:
DES-1210-28/ME:5# config dhcp_relay delete ipif System 10.6.150.49
Command: config dhcp_relay delete ipif System 10.6.150.49
Success!
DES-1210-28/ME:5#
config dhcp_relay
Purpose To delete a DHCP server from the DHCP Relay server list.
Syntax
config dhcp_relay hops <value 1-16>
Description
The config dhcp_relay hops command configures the
DHCP/BOOTP relay feature.
Parameters
hops <value 1-16> − Specifies the maximum number of relay agent
hops that the DHCP packets can cross.
Restrictions Only Administrator or operate-level users can issue this command.
Example usage:
To configure the DHCP relay on the Switch:
DES-1210-28/ME:5# config dhcp_relay hops 12
Command: config dhcp_relay hops 12
Success!
DES-1210-28/ME:5#
Page 97
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
85
config dhcp_relay option_82
Purpose To configure the check, policy and state of DHCP relay agent
information option 82 of the Switch.
Syntax
config dhcp_relay option_82 [check [enable | disable] | policy
[drop | keep | replace] | remote_id [default | user_define <string
32>] | state [enable | disable]]
Description
The config dhcp_relay option_82 is used to configure the check,
policy and state of DHCP relay agent information option 82 of the
Switch
Parameters
check: used to configure the check of DHCP relay agent information
option 82 of the Switch.
enable – When the field is toggled to enable, the relay agent will
check the validity of the packet’s option 82 field. If the switch
receives a packet that contains the option 82 field from a DHCP
client, the switch drops the packet because it is invalid. In packets
received from DHCP servers, the relay agent will drop invalid
messages.
disable – When the field is toggled to disable, the relay agent will not
check the validity of the packet’s option 82 field.
policy: used to configure the re-forwarding policy of DHCP relay
agent information option 82 of the Switch.
replace − The option 82 field will be replaced if the option 82 field
already exists in the packet received from the DHCP client.
drop − The packet will be dropped if the option 82 field already
exists in the packet received from the DHCP client.
keep − The option 82 field will be retained if the option 82 field
already exists in the packet received from the DHCP client.
state: used to configure the state of DHCP relay agent information
option 82 of the Switch.
enable − W hen this field is toggled to Enabled the relay agent will
insert and remove DHCP relay information (option 82 field) in
messages between DHCP server and client. When the relay agent
receives the DHCP request, it adds the option 82 information, and
the IP address of the relay agent (if the relay agent is configured), to
the packet. Once the option 82 information has been added to the
packet it is sent on to the DHCP server. When the DHCP server
receives the packet, if the server is capable of option 82, it can
implement policies like restricting the number of IP addresses that
can be assigned to a single remote ID or circuit ID. Then the DHCP
server echoes the option 82 field in the DHCP reply. The DHCP
server unicasts the reply to the back to the relay agent if the request
was relayed to the server by the relay agent. The switch verifies that
it originally inserted the option 82 data. Finally, the relay agent
removes the option 82 field and forwards the packet to the switch
port that connects to the DHCP client that sent the DHCP request.
disable − If the field is toggled to disable the relay agent will not
insert and remove DHCP relay information (option 82 field) in
messages between DHCP servers and clients, and the check and
policy settings will have no effect.
Restrictions Only Administrator or operate-level users can issue this command.
Page 98
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
86
Example usage:
To disable the DHCP relay option 82 on the Switch:
DES-1210-28/ME:5# config dhcp_relay option_82 state disable
Command: config dhcp_relay option_82 state disable
Success!
DES-1210-28/ME:5#
show dhcp_relay
Purpose To
display the DHCP Relay settings on the Switch
.
Syntax
show dhcp_relay {ipif}
Description
The show dhcp_relay command displays the DHCP Relay status
and list of servers defined as DHCP Relay servers on the Switch.
Parameters None.
Restrictions None.
Example usage:
To display DHCP Relay settings:
DES-1210-28/ME:5# show dhcp_relay
Command: show dhcp_relay
DHCP/BOOTP Relay Status : Disabled
DHCP/BOOTP Hops Count Limit : 4
DHCP/BOOTP Relay Time Threshold : 0
DHCP Relay Agent Information Option 82 State : Disabled
DHCP Relay Agent Information Option 82 Check : Disabled
DHCP Relay Agent Information Option 82 Policy : Replace
DHCP Relay Agent Information Option 82 ID : 00-B2-FD-DA-EE-EB
Interface Server 1 Server 2 Server 3 Server 4
--------- --------------- --------------- -------------- --------------DES-1210-28/ME:5#
enable dhcp_local_relay
Purpose To enable the DHCP local relay feature globally
Syntax
enable dhcp_local_relay
Description
The enable dhcp_local_relay command enables the DHCP local
relay feature on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command
Example usage:
Page 99
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
87
To enable the DHCP Local Relay:
DES-1210-28/ME:5# enable dhcp_local_relay
Command: enable dhcp_local_relay
Success
DES-1210-28/ME:5#
disable dhcp_local_relay
Purpose To disable the DHCP local relay feature globally
Syntax
disable dhcp_local_relay
Description
The disable dhcp_local_relay command disables the DHCP local
relay feature on the Switch.
Parameters None.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable the DHCP Local Relay:
DES-1210-28/ME:5# disable dhcp_local_relay
Command: disable dhcp_local_relay
Success
DES-1210-28/ME:5#
config dhcp_local_relay vlan
Purpose To specify which VLAN’s the feature works on.
Syntax
config dhcp_local_relay vlan <vlan_name> | vlanid <vidlist>]
state[enable | disable]
Description Each VLAN which was added to the DHCP Local Relay list
participates in the DHCP Local Relay process – Option 82 is added
to DHCP requests on this VLAN, and Removed from DHCP Replies
on this VLAN.
Parameters
vlan_name – the VLAN name identifier
vlanid <vidlist> – The VLAN tag identifier
state [enable | disable] – enable or disable of the DHCP Local Relay
status by VLAN name or VLAN ID.
Restrictions Only Administrator or operator-level users can issue this command.
Example usage:
To disable the VLAN ID10 from VLAN of DHCP Local Relay:
DES-1210-28/ME:5# config dhcp_local_relay vlan vlanid 10 state disable
Command: config dhcp_local_relay vlan vlanid 10 state disable
Page 100
DES-1210-28/ME Metro Ethernet Managed Switch CLI Reference Guide
88
Success
DES-1210-28/ME:5#
show dhcp_local_relay
Purpose To display which VLAN’s the feature works on.
Syntax
show dhcp_local_relay
Description Each VLAN which was added to the DHCP Local Relay list
participates in the DHCP Local Relay process – Option 82 is added
to DHCP requests on this VLAN, and Removed from DHCP Replies
on this VLAN.
Parameters None.
Restrictions None.
Example usage:
To display the DHCP local relay information on the Switch:
DES-1210-28/ME:5# show dhcp_local_relay
Command: show dhcp_local_relay
DHCP/BOOTP Local Relay Status : Disabled
DHCP/BOOTP Local Relay VID List :
DES-1210-28/ME:5#
 Loading...