

Page 1
DES-3550
Layer 2 Switch
Command Line Interface Reference Manual
First Edition (February 2004)
651ES3550015
Printed In Taiwan
RECYCLABLE
Page 2
Wichtige Sicherheitshinweise
1. Bitte lesen Sie sich diese Hinweise sorgfältig durch.
2. Heben Sie diese Anleitung für den spätern Gebrauch auf.
3. Vor jedem Reinigen ist das Gerät vom Stromnetz zu trennen. Vervenden Sie keine Flüssig- oder Aerosolreiniger. Am besten dient ein angefeuchtetes
Tuch zur Reinigung.
4. Um eine Beschädigung des Gerätes zu vermeiden sollten Sie nur Zubehörteile verwenden, die vom Hersteller zugelassen sind.
5. Das Gerät is vor Feuchtigkeit zu schützen.
6. Bei der Aufstellung des Gerätes ist auf sichern Stand zu achten. Ein Kippen oder Fallen könnte Verletzungen hervorrufen. Verwenden Sie nur sichere
Standorte und beachten Sie die Aufstellhinweise des Herstellers.
7. Die Belüftungsöffnungen dienen zur Luftzirkulation die das Gerät vor Überhitzung schützt. Sorgen Sie dafür, daß diese Öffnungen nicht abgedeckt
werden.
8. Beachten Sie beim Anschluß an das Stromnetz die Anschlußwerte.
9. Die Netzanschlußsteckdose muß aus Gründen der elektrischen Sicherheit einen Schutzleiterkontakt haben.
10. Verlegen Sie die Netzanschlußleitung so, daß niemand darüber fallen kann. Es sollete auch nichts auf der Leitung abgestellt werden.
11. Alle Hinweise und Warnungen die sich am Geräten befinden sind zu beachten.
12. Wird das Gerät über einen längeren Zeitraum nicht benutzt, sollten Sie es vom Stromnetz trennen. Somit wird im Falle einer Überspannung eine
Beschädigung vermieden.
13. Durch die Lüftungsöffnungen dürfen niemals Gegenstände oder Flüssigkeiten in das Gerät gelangen. Dies könnte einen Brand bzw. Elektrischen Schlag
auslösen.
14. Öffnen Sie niemals das Gerät. Das Gerät darf aus Gründen der elektrischen Sicherheit nur von authorisiertem Servicepersonal geöffnet werden.
15. Wenn folgende Situationen auftreten ist das Gerät vom Stromnetz zu trennen und von einer qualifizierten Servicestelle zu überprüfen:
a – Netzkabel oder Netzstecker sint beschädigt.
b – Flüssigkeit ist in das Gerät eingedrungen.
c – Das Gerät war Feuchtigkeit ausgesetzt.
d – Wenn das Gerät nicht der Bedienungsanleitung ensprechend funktioniert oder Sie mit Hilfe dieser Anleitung keine Verbesserung erzielen.
e – Das Gerät ist gefallen und/oder das Gehäuse ist beschädigt.
f – Wenn das Gerät deutliche Anzeichen eines Defektes aufweist.
16. Bei Reparaturen dürfen nur Orginalersatzteile bzw. den Orginalteilen entsprechende Teile verwendet werden. Der Einsatz von ungeeigneten Ersatzteilen
kann eine weitere Beschädigung hervorrufen.
17. Wenden Sie sich mit allen Fragen die Service und Repartur betreffen an Ihren Servicepartner. Somit stellen Sie die Betriebssicherheit des Gerätes sicher.
18. Zum Netzanschluß dieses Gerätes ist eine geprüfte Leitung zu verwenden, Für einen Nennstrom bis 6A und einem Gerätegewicht grőßer 3kg ist eine
Leitung nicht leichter als H05VV-F, 3G, 0.75mm2 einzusetzen.
WARRANTIES EXCLUSIVE
IF THE D-LINK PRODUCT DOES NOT OPERATE AS WARRANTED ABOVE, THE CUSTOMER'S SOLE REMEDY SHALL BE, AT
D-LINK'S OPTION, REPAIR OR REPLACEMENT. THE FOREGOING WARRANTIES AND REMEDIES ARE EXCLUSIVE AND ARE
IN LIEU OF ALL OTHER WARRANTIES, EXPRESSED OR IMPLIED, EITHER IN FACT OR BY OPERATION OF LAW,
STATUTORY OR OTHERWISE, INCLUDING WARRANTIES OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR
PURPOSE. D-LINK NEITHER ASSUMES NOR AUTHORIZES ANY OTHER PERSON TO ASSUME FOR IT ANY OTHER LIABILITY
IN CONNECTION WITH THE SALE, INSTALLATION MAINTENANCE OR USE OF D-LINK'S PRODUCTS
D-LINK SHALL NOT BE LIABLE UNDER THIS WARRANTY IF ITS TESTING AND EXAMINATION DISCLOSE THAT THE
ALLEGED DEFECT IN THE PRODUCT DOES NOT EXIST OR WAS CAUSED BY THE CUSTOMER'S OR ANY THIRD PERSON'S
MISUSE, NEGLECT, IMPROPER INSTALLATION OR TESTING, UNAUTHORIZED ATTEMPTS TO REPAIR, OR ANY OTHER
CAUSE BEYOND THE RANGE OF THE INTENDED USE, OR BY ACCIDENT, FIRE, LIGHTNING OR OTHER HAZARD.
LIMITATION OF LIABILITY
IN NO EVENT WILL D-LINK BE LIABLE FOR ANY DAMAGES, INCLUDING LOSS OF DATA, LOSS OF PROFITS, COST OF
COVER OR OTHER INCIDENTAL, CONSEQUENTIAL OR INDIRECT DAMAGES ARISING OUT THE INSTALLATION,
MAINTENANCE, USE, PERFORMANCE, FAILURE OR INTERRUPTION OF A D- LINK PRODUCT, HOWEVER CAUSED AND ON
ANY THEORY OF LIABILITY. THIS LIMITATION WILL APPLY EVEN IF D-LINK HAS BEEN ADVISED OF THE POSSIBILITY OF
SUCH DAMAGE.
IF YOU PURCHASED A D-LINK PRODUCT IN THE UNITED STATES, SOME STATES DO NOT ALLOW THE LIMITATION OR
EXCLUSION OF LIABILITY FOR INCIDENTAL OR CONSEQUENTIAL DAMAGES, SO THE ABOVE LIMITATION MAY NOT
APPLY TO YOU.
ii
Page 3
Limited Warranty
Hardware:
D-Link warrants each of its hardware products to be free from defects in workmanship and materials under normal use and service for a period
commencing on the date of purchase from D-Link or its Authorized Reseller and extending for the length of time stipulated by the Authorized
Reseller or D-Link Branch Office nearest to the place of purchase.
This Warranty applies on the condition that the product Registration Card is filled out and returned to a D-Link office within ninety (90) days
of purchase. A list of D-Link offices is provided at the back of this manual, together with a copy of the Registration Card.
If the product proves defective within the applicable warranty period, D-Link will provide repair or replacement of the product. D-Link shall
have the sole discretion whether to repair or replace, and replacement product may be new or reconditioned. Replacement product shall be of
equivalent or better specifications, relative to the defective product, but need not be identical. Any product or part repaired by D-Link
pursuant to this warranty shall have a warranty period of not less than 90 days, from date of such repair, irrespective of any earlier expiration
of original warranty period. When D-Link provides replacement, then the defective product becomes the property of D-Link.
Warranty service may be obtained by contacting a D-Link office within the applicable warranty period, and requesting a Return Material
Authorization (RMA) number. If a Registration Card for the product in question has not been returned to D-Link, then a proof of purchase
(such as a copy of the dated purchase invoice) must be provided. If Purchaser's circumstances require special handling of warranty correction,
then at the time of requesting RMA number, Purchaser may also propose special procedure as may be suitable to the case.
After an RMA number is issued, the defective product must be packaged securely in the original or other suitable shipping package to ensure
that it will not be damaged in transit, and the RMA number must be prominently marked on the outside of the package. The package must be
mailed or otherwise shipped to D-Link with all costs of mailing/shipping/insurance prepaid. D-Link shall never be responsible for any
software, firmware, information, or memory data of Purchaser contained in, stored on, or integrated with any product returned to D-Link
pursuant to this warranty.
Any package returned to D-Link without an RMA number will be rejected and shipped back to Purchaser at Purchaser's expense, and D-Link
reserves the right in such a case to levy a reasonable handling charge in addition mailing or shipping costs.
Software:
Warranty service for software products may be obtained by contacting a D-Link office within the applicable warranty period. A list of D-Link
offices is provided at the back of this manual, together with a copy of the Registration Card. If a Registration Card for the product in question
has not been returned to a D-Link office, then a proof of purchase (such as a copy of the dated purchase invoice) must be provided when
requesting warranty service. The term "purchase" in this software warranty refers to the purchase transaction and resulting license to use such
software.
D-Link warrants that its software products will perform in substantial conformance with the applicable product documentation provided by
D-Link with such software product, for a period of ninety (90) days from the date of purchase from D-Link or its Authorized Reseller. D-Link
warrants the magnetic media, on which D-Link provides its software product, against failure during the same warranty period. This warranty
applies to purchased software, and to replacement software provided by D-Link pursuant to this warranty, but shall not apply to any update or
replacement which may be provided for download via the Internet, or to any update which may otherwise be provided free of charge.
D-Link's sole obligation under this software warranty shall be to replace any defective software product with product which substantially
conforms to D-Link's applicable product documentation. Purchaser assumes responsibility for the selection of appropriate application and
system/platform software and associated reference materials. D-Link makes no warranty that its software products will work in combination
with any hardware, or any application or system/platform software product provided by any third party, excepting only such products as are
expressly represented, in D-Link's applicable product documentation as being compatible. D-Link's obligation under this warranty shall be a
reasonable effort to provide compatibility, but D-Link shall have no obligation to provide compatibility when there is fault in the third-party
hardware or software. D-Link makes no warranty that operation of its software products will be uninterrupted or absolutely error-free, and no
warranty that all defects in the software product, within or without the scope of D-Link's applicable product documentation, will be corrected.
iii
Page 4
Subject to the terms and conditions set forth herein, D-Link Systems, Inc. (“D-Link”) provides this Limited warranty for its product only to the person
or entity that originally purchased the product from:
D-Link or its authorized reseller or distributor and
Products purchased and delivered within the fifty states of the United States, the District of Columbia, U.S. Possessions or Protectorates,
and U.S. Military Installations, addresses with an APO or FPO.
Limited Warranty:
workmanship and materials from the date of original retail purchase of the product, for the period set forth below applicable to the product type
(“Warranty Period”), except as otherwise state d herein.
D-Link warrants that the hardware portion of the D-Link products described below will be free from material defects in
5-Year Limited Warranty for the Product(s) is defined as follows:
Hardware (excluding power supplies and fans) Five (5) Years
Power Supplies and Fans Three (3) Year
Spare parts and spare kits Ninety (90) days
D-Link’s sole obligation shall be to repair or replace the defective Hardware during the Warranty Period at no charge to the original owner or to
refund at D-Link’s sole discretion. Such repair or replacement will be rendered by D-Link at an Authorized D-Link Service Office. The replacement
Hardware need not be new or have an identical make, model or part. D-Link may in its sole discretion replace the defective Hardware (or any part
thereof) with any reconditioned product that D-Link reasonably determines is substantially equivalent (or superior) in all material respects to the
defective Hardware. Repaired or replacement Hardware will be warranted for the remainder of the original Warranty Period from the date of original
retail purchase. If a material defect is incapable of correction, or if D-Link determines in its sole discretion that it is not practical to repair or replace
the defective Hardware, the price paid by the original purchaser for the defective Hardware will be refunded by D-Link upon return to D-Link of the
defective Hardware. All Hardware (or part thereof) that is replaced by D-Link, or for which the purchase price is refunded, shall become the property
of D-Link upon replacement or refund.
Limited Software Warranty:
current functional specifications for the Software, as set forth in the applicable documentation, from the date of original retail purchase of the
Software for a period of ninety (90) days (“Warranty Period”), provided that the Software is properly installed on approved hardware and operated as
contemplated in its documentation. D-Link further warrants that, during the Warranty Period, the magnetic media on which D-Link delive rs the
Software will be free of physical defects. D-Link’s sole obligation shall be to replace the non-conforming Software (or defective media) with software
that substantially conforms to D-Link’s functional specifications for the Software or to refund at D-Link’s sole discretion. Except as otherwise agreed
by D-Link in writing, the replacement Software is provided only to the original licensee, and is subject to the terms and conditions of the license
granted by D-Link for the Software. Software will be warranted for the remainder of the original Warranty Period from the date or original retail
purchase. If a material non-conformance is incapable of correction, or if D-Link determines in its sole discretion that it is not practical to replace the
non-conforming Software, the price paid by the original licensee for the non-conforming Software will be refunded by D-Link; provided that the nonconforming Software (and all copies thereof) is first returned to D-Link. The license granted respecting any Software for which a refund is given
automatically terminates.
Non-Applicability of Warranty: The Limited Warranty provided hereunder for hardware and software of D-Link's products, will not be applied to
and does not cover any product purchased through the inventory clearance or liquidation sale or other sales in which D-Link, the sellers, or the
liquidators expressly disclaim their warranty obligation pertaining to the product and in that case, the product is being sold "As-Is" without any
warranty whatsoever including, without limitation, the Limited Warranty as described herein, notwithstanding anything stated herein to the contrary.
Submitting A Claim: Any claim under this limited warranty must be submitted in writing before the end of the Warranty Period to an Authorized DLink Service Office.
The customer must submit as part of the claim a written description of the Hardware defect or Software nonconformance in sufficient
detail to allow D-Link to confirm the same.
The original product owner must obtain a Return Material Authorization (“RMA”) number from the Authorized D-Link Service Office and, if
requested, provide written proof of purchase of the product (such as a copy of the dated purchase invoice for the product) before the
warranty service is provided.
After an RMA number is issued, the defective product must be packaged securely in the original or other suitable shipping package to
ensure that it will not be damaged in transit, and the RMA number must be prominently marked on the outside of the package. Do not
include any manuals or accessories in the shipping package. D-Link will only replace the defective portion of the Product and will not ship
back any accessories.
The customer is responsible for all shipping charges to D-Link. No Charge on Delivery (“COD”) is allowed. Products sent COD will either
be rejected by D-Link or become the property of D-Link. Products should be fully insured by the customer and shipped to D-Link Systems,
Inc., 53 Discovery Drive, Irvine, CA 92618. D-Link will not be held responsible for any packages that are lost in transit to D-Link. The
repaired or replaced packages will be shipped via UPS Ground or any common carrier selected by D-Link, with shipping charges prepaid.
Expedited shipping is available if shipping charges are prepaid by the customer.
D-Link may reject or return any product that is not packaged and shipped in strict compliance with the foregoing requirements, or for which an RMA
number is not visible from the outside of the package. The product owner agrees to pay D-Link’s reasonable handling and return shipping charges for
any product that is not packaged and shipped in accordance with the foregoing requirements, or that is determine d by D-Link not to be defective or
non-conforming.
What Is Not Covered: This limited warranty provided by D-Link does not cover: Products, if in D-Link’s judgment, have been subjected to abuse,
accident, alteration, modification, tampering, negligence, misuse, faulty installation, lack of reasonable care, repair or service in any way that is not
contemplated in the documentation for the product, or if the model or serial number has been altered, tampered with, defaced or removed; Initial
installation, installation and removal of the product for repair, and shipping costs; Operational adjustments covered in the operating manual for the
product, and normal maintenance; Damage that occurs in shipment, due to act of God, failures due to power surge, and cosmetic damage; Any
hardware, software, firmware or other products or services provided by anyone other than D-Link; Products that have been purchased from
D-Link warrants that the software portion of the product (“Software”) will substantially conform to D-Link’s then
iv
Page 5
inventory clearance or liquidation sales or other sales in which D-Link, the sellers, or the liquidators e xpressly disclaim their warranty obligation
pertaining to the product. Repair by anyone other than D-Link or an Authorized D-Link Service Office will void this Warranty.
Disclaimer of Other Warranties: EXCEPT FOR THE LIMITED WARRANTY SPECIFIED HEREIN, THE PRODUCT IS PROVIDED “AS-IS” WITHOUT
ANY WARRANTY OF ANY KIND WHATSOEVER INCLUDING, WITHOUT LIMITATION, ANY WARRANTY OF MERCHANTABILITY, FITNESS FOR A
PARTICULAR PURPOSE AND NON-INFRINGEMENT. IF ANY IMPLIED WARRANTY CANNOT BE DISCLAIMED IN ANY TERRITORY WHERE A
PRODUCT IS SOLD, THE DURATION OF SUCH IMPLIED WARRANTY SHALL BE LIMITED TO NINETY (90) DAYS. EXCEPT AS EXPRESSLY COVERED
UNDER THE LIMITED WARRANTY PROVIDED HEREIN, THE ENTIRE RISK AS TO THE QUALITY, SELECTION AND PERFORMANCE OF THE
PRODUCT IS WITH THE PURCHASER OF THE PRODUCT.
Limitation of Liability: TO THE MAXIMUM EXTENT PERMITTED BY LAW, D-LINK IS NOT LIABLE UNDER ANY CONTRACT, NEGLIGENCE, STRICT
LIABILITY OR OTHER LEGAL OR EQUITABLE THEORY FOR ANY LOSS OF USE OF THE PRODUCT, INCONVENIENCE OR DAMAGES OF ANY
CHARACTER, WHETHER DIRECT, SPECIAL, INCIDENTAL OR CONSEQUENTIAL (INCLUDING, BUT NOT LIMITED TO, DAMAGES FOR LOSS OF
GOODWILL, LOSS OF REVENUE OR PROFIT, WORK STOPPAGE, COMPUTER FAILURE OR MALFUNCTION, FAILURE OF OTHER EQUIPMENT OR
COMPUTER PROGRAMS TO WHICH D-LINK’S PRODUCT IS CONNECTED WITH, LOSS OF INFORMATION OR DATA CONTAINED IN, STORED ON,
OR INTEGRATED WITH ANY PRODUCT RETURNED TO D-LINK FOR WARRANTY SERVICE) RESULTING FROM THE USE OF THE PRODUCT,
RELATING TO WARRANTY SERVICE, OR ARISING OUT OF ANY BREACH OF THIS LIMITED WARRANTY, EVEN IF D-LINK HAS BEEN ADVISED OF
THE POSSIBILITY OF SUCH DAMAGES. THE SOLE REMEDY FOR A BREACH OF THE FOREGOING LIMITED WARRANTY IS REPAIR,
REPLACEMENT OR REFUND OF THE DEFECTIVE OR NON-CONFORMING PRODUCT. THE MAXIMUM LIABILITY OF D-LINK UNDER THIS
WARRANTY IS LIMITED TO THE PURCHASE PRICE OF THE PRODUCT COVERED BY THE WARRANTY. THE FOREGOING EXPRESS WRITTEN
WARRANTIES AND REMEDIES ARE EXCLUSIVE AND ARE IN LIEU OF ANY OTHER WARRANTIES OR REMEDIES, EXPRESS, IMPLIED OR
STATUTORY.
Governing Law: This Limited Warranty shall be governed by the laws of the state of California. Some states do not allow
exclusion or limitation of incidental or consequential damages, or limitations on how long an implied warranty lasts, so the
foregoing limitations and exclusions may not apply. This limited warranty provides specific legal rights and the product owner
may also have other rights which vary from state to state
For detailed warranty outside the United States, please contact corresponding local D-Link office.
Register online your D-Link product at http://support.dlink.com/register/
D-Link Offices for Registration and Warranty Service
The product's Registration Card, provided at the back of this manual, must be sent to a D-Link office. To obtain an RMA number for warranty
service as to a hardware product, or to obtain warranty service as to a software product, contact the D-Link office nearest you. An
address/telephone/fax/e-mail/Web site list of D-Link offices is provided in the back of this manual.
Trademarks
Copyright 2003 D-Link Corporation.
Contents subject to change without prior notice.
D-Link is a registered trademark of D-Link Corporation/D-Link Systems, Inc. All other trademarks belong to their respective proprietors.
Copyright Statement
No part of this publication may be reproduced in any form or by any means or used to make any derivative such as translation, transformation,
or adaptation without permission from D-Link Corporation/D-Link Systems Inc., as stipulated by the United States Copyright Act of 1976.
FCC Warning
This equipment has been tested and found to comply with the limits for a Class A digital device, pursuant to Part 15 of the FCC
Rules. These limits are designed to provide reasonable protection against harmful interference when the equipment is operated
in a commercial environment. This equipment generates, uses, and can radiate radio frequency energy and, if not installed and
used in accordance with this user’s guide, may cause harmful interference to radio communications. Operation of this
equipment in a residential area is likely to cause harmful interference in which case the user will be required to correct the
interference at his own expense.
CE Mark Warning
This is a Class A product. In a domestic environment, this product may cause radio interference in which case the user may be
required to take adequate measures.
VCCI Warning
v
Page 6

Page 7
Table of Contents
Introduction...................................................................................................................................................................................... 1
Using the Console CLI..................................................................................................................................................................... 4
Command Syntax............................................................................................................................................................................. 8
Basic Switch Commands................................................................................................................................................................ 10
Switch Port Commands.................................................................................................................................................................. 21
Port Security Commands................................................................................................................................................................ 24
Network Management (SNMP) Commands .................................................................................................................................. 27
Switch Utility Commands .............................................................................................................................................................. 49
Network Monitoring Commands ................................................................................................................................................... 53
Spanning Tree Commands............................................................................................................................................................. 66
Forwarding Database Commands .................................................................................................................................................. 72
Broadcast Storm Control Commands............................................................................................................................................. 80
QoS Commands ............................................................................................................................................................................. 82
Port Mirroring Commands............................................................................................................................................................. 90
VLAN Commands.......................................................................................................................................................................... 94
Asymmetric VLAN Commands................................................................................................................................................... 100
Link Aggregation Commands ...................................................................................................................................................... 102
Basic IP Commands ..................................................................................................................................................................... 108
IGMP Snooping Commands ........................................................................................................................................................ 110
802.1X Commands....................................................................................................................................................................... 120
Access Control List (ACL) Commands ....................................................................................................................................... 132
Traffic Segmentation Commands................................................................................................................................................. 143
Time and SNTP Commands......................................................................................................................................................... 145
ARP Commands........................................................................................................................................................................... 152
Routing Table Commands............................................................................................................................................................156
MAC Notification Commands ..................................................................................................................................................... 158
Access Authentication Control Commands.................................................................................................................................. 162
Page 8
Single IP Management Commands...............................................................................................................................................187
Command History List..................................................................................................................................................................198
Technical Specifications...............................................................................................................................................................201
Page 9
1
INTRODUCTION
The Switch can be managed through the Switch’s serial port, Telnet, or the Web-based management agent. The Command Line
Interface (CLI) can be used to configure and manage the Switch via the serial port or Telnet interfaces.
This manual provides a reference for all of the commands contained in the CLI. Configuration and management of the switch
via the Web-based management agent is discussed in the User’s Guide.
Accessing the Switch via the Serial Port
The Switch’s serial port’s default settings are as follows:
• 9600 baud
• no parity
• 8 data bits
• 1 stop bit
A computer running a terminal emulation program capable of emulating a VT-100 terminal and a serial port configured as
above is then connected to the Switch’s serial port via an RS-232 DB-9 cable.
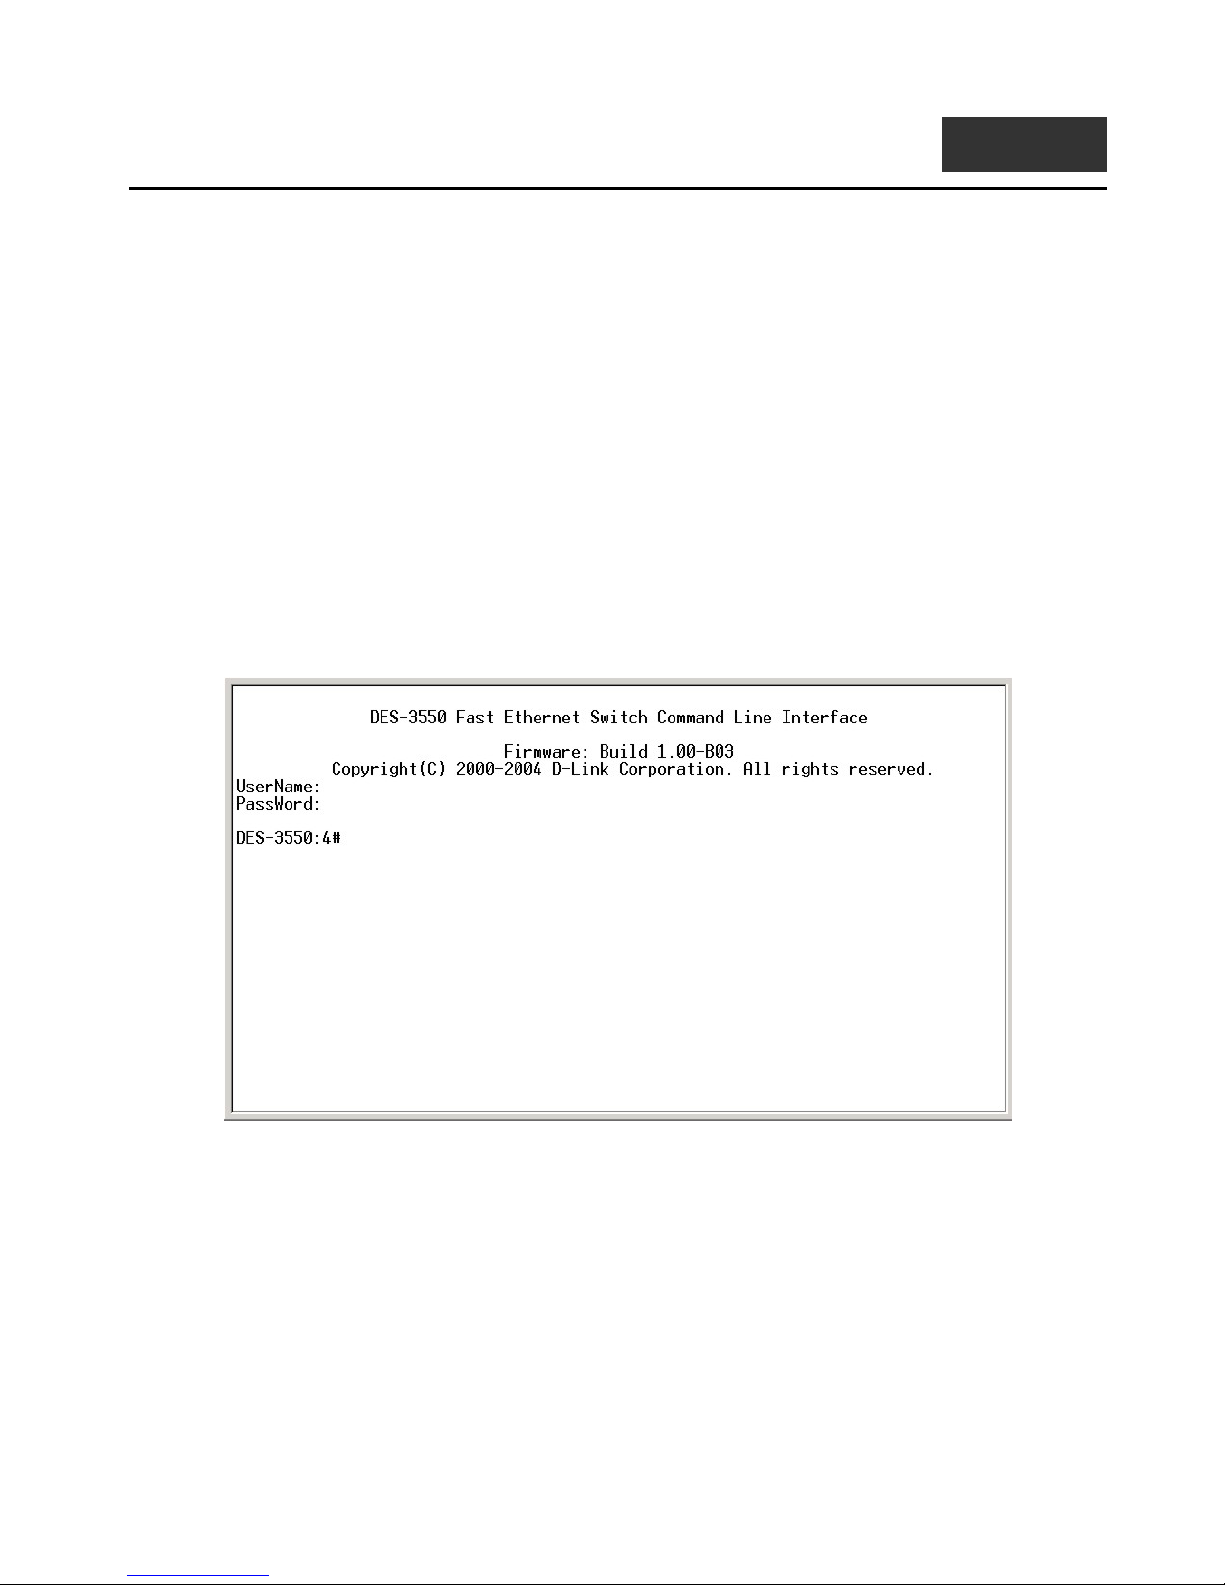
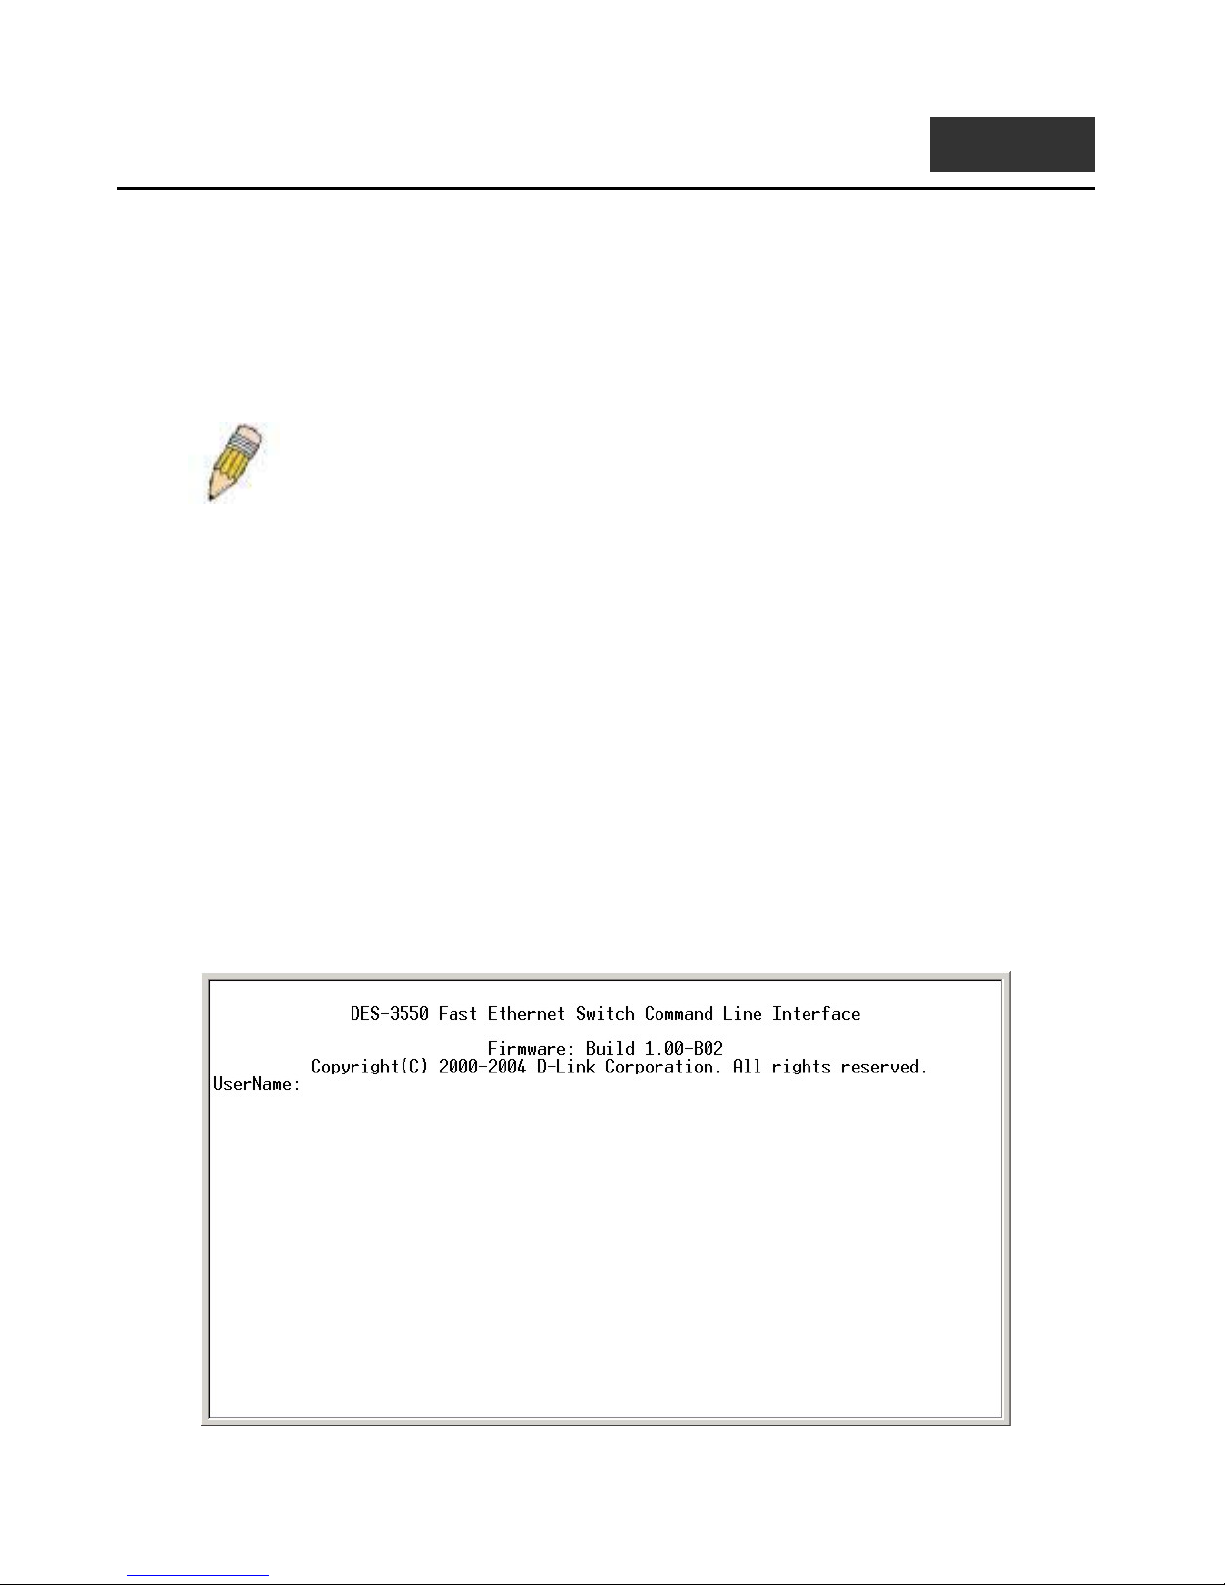
With the serial port properly connected to a management computer, the following screen should be visible. If this screen does
not appear, try pressing Ctrl+r to refresh the console screen.
There is no initial username or password. Just press the Enter key twice to display the CLI input cursor − DES-3550:4#. This is
the command line where all commands are input.
Setting the Switch’s IP Address
Each Switch must be assigned its own IP Address, which is used for communication with an SNMP network manager or other
TCP/IP application (for example BOOTP, TFTP). The Switch’s default IP address is 10.90.90.90. You can change the default
Switch IP address to meet the specification of your networking address scheme.
The Switch is also assigned a unique MAC address by the factory. This MAC address cannot be changed, and can be found on
the initial boot console screen – shown below.
Figure 1-1. Initial CLI screen
1
Page 10

Figure 1-2. Boot Screen
The Switch’s MAC address can also be found in the Web management program on the Switch Information (Basic Settings)
window on the Configuration menu.
The IP address for the switch must be set before it can be managed with the Web-based manager. The Switch IP address can be
automatically set using BOOTP or DHCP protocols, in which case the actual address assigned to the switch must be known.
The IP address may be set using the Command Line Interface (CLI) over the console serial port as follows:
1. Starting at the command line prompt, enter the commands config ipif System ipaddress
xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy
. Where the x’s represent the IP address to be assigned to the IP interface named
System and the y’s represent the corresponding subnet mask.
2. Alternatively, you can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x’s represent the IP address
to be assigned to the IP interface named System and the z represents the corresponding number of subnets in CIDR
notation.
The IP interface named System on the switch can be assigned an IP address and subnet mask which can then be used to connect
a management station to the switch’s Telnet or Web-based management agent.
Figure 1-3. Assigning an IP Address
2
Page 11
In the above example, the Switch was assigned an IP address of 10.53.13.144/8 with a subnet mask of 255.0.0.0. The system
message Success indicates that the command was executed successfully. The Switch can now be configured and managed via
Telnet, SNMP MIB browser and the CLI or via the Web-based management agent using the above IP address to connect to the
Switch.
3
Page 12
2
USING THE CONSOLE CLI
The DES-3550 supports a console management interface that allows the user to connect to the switch’s management agent via a
serial port and a terminal or a computer running a terminal emulation program. The console can also be used over the network
using the TCP/IP Telnet protocol. The console program can be used to configure the Switch to use an SNMP-based network
management software over the network.
This chapter describes how to use the console interface to access the switch, change its settings, and monitor its operation.
: Switch configuration settings are saved to non-volatile RAM using
Note
the save command. The current configuration will then be retained in the
switch’s NV-RAM, and reloaded when the Switch is rebooted. If the Switch
is rebooted without using the save command, the last configuration saved
to NV-RAM will be loaded.
Connecting to the Switch
The console interface is used by connecting the Switch to a VT100-compatible terminal or a computer running an ordinary
terminal emulator program (e.g., the HyperTerminal program included with the Windows operating system) using an RS-232C
serial cable. Your terminal parameters will need to be set to:
• VT-100 compatible
• 9600 baud
• 8 data bits
• No parity
• One stop bit
• No flow control
You can also access the same functions over a Telnet interface. Once you have set an IP address for your Switch, you can use a
Telnet program (in VT-100 compatible terminal mode) to access and control the Switch. All of the screens are identical,
whether accessed from the console port or from a Telnet interface.
After the Switch reboots and you have logged in, the console looks like this:
Figure 2-1. Initial Console Screen
4
Page 13
Commands are entered at the command prompt, DES-3550:4#.
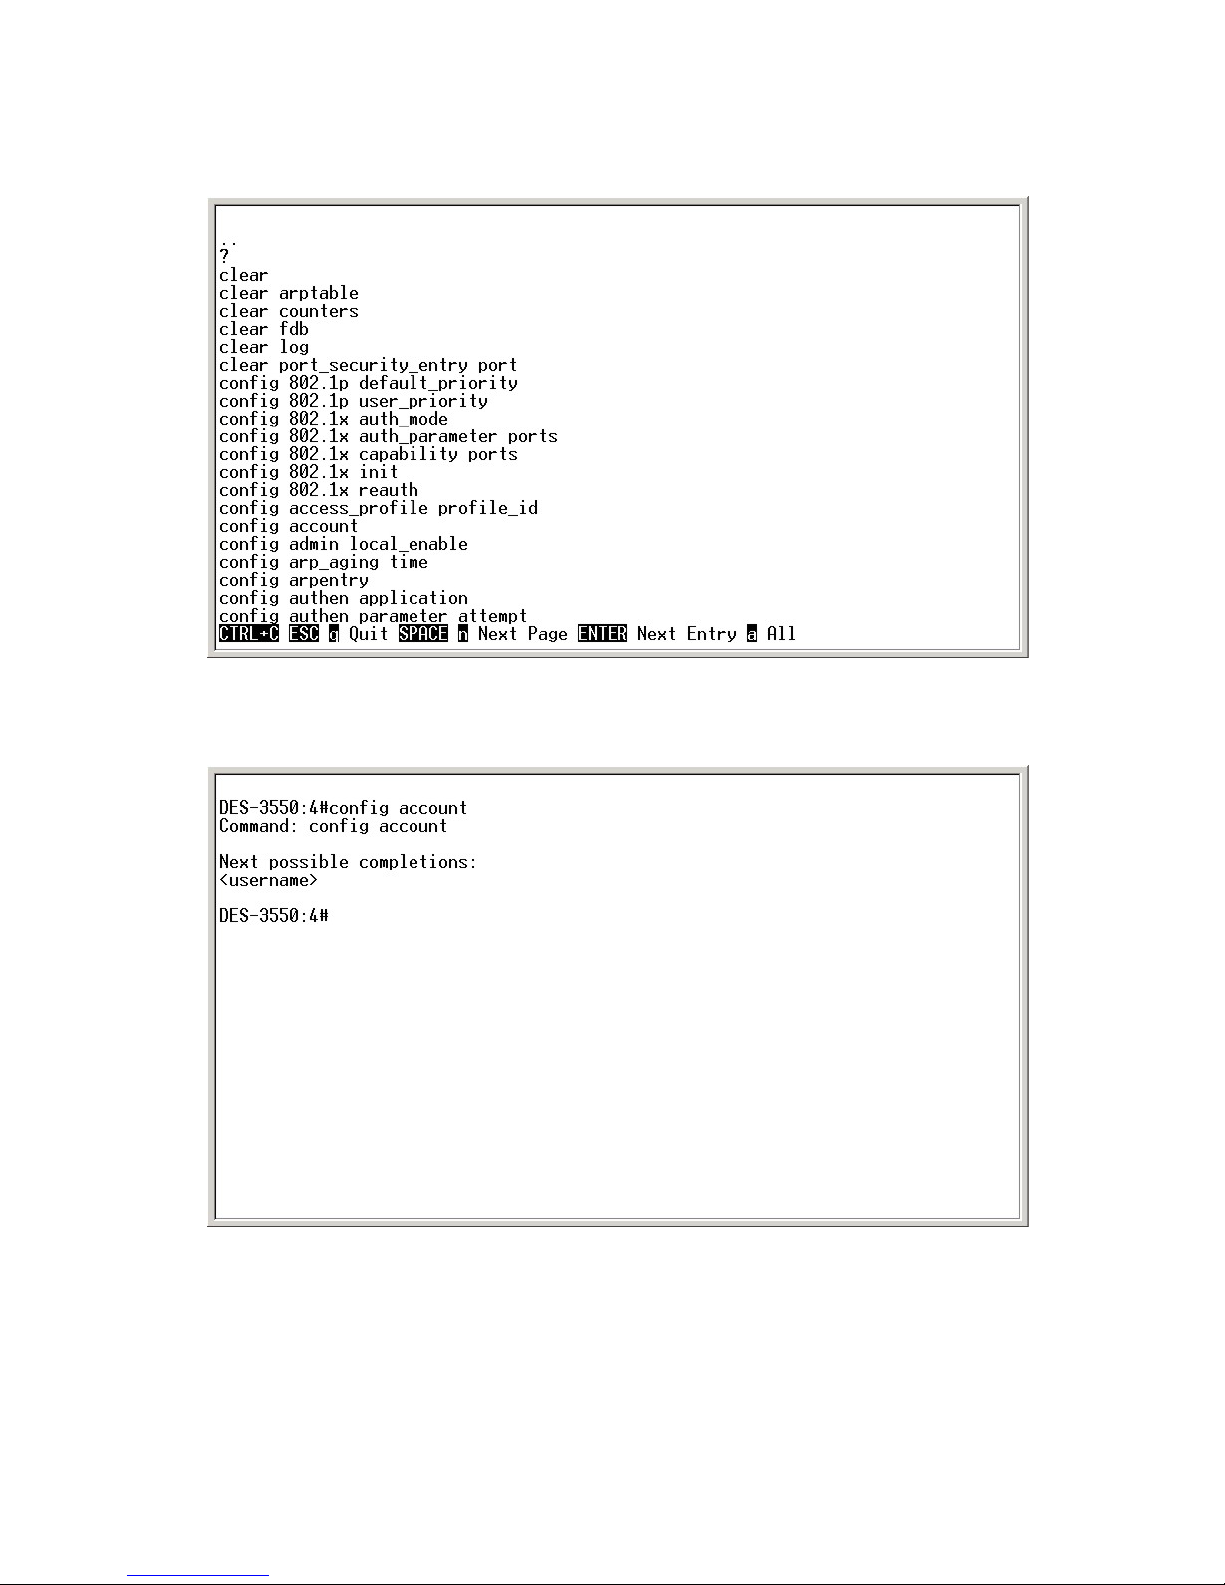
There are a number of helpful features included in the CLI. Entering the ? command will display a list of all of the top-level
commands.
Figure 2-2. The ? Command
When you enter a command without its required parameters, the CLI will prompt you with a
Next possible completions:
message.
Figure 2-3. Example Command Parameter Help
In this case, the command
config account
was entered with the parameter
<username>
. The CLI will then prompt you to enter
the <username> with the message, Next possible completions:. Every command in the CLI has this feature, and complex
commands have several layers of parameter prompting.
In addition, after typing any given command plus one space, you can see all of the next possible sub-commands, in sequential
order, by repeatedly pressing the Tab key.
To re-enter the previous command at the command prompt, press the up arrow cursor key. The previous command will appear at
the command prompt.
5
Page 14
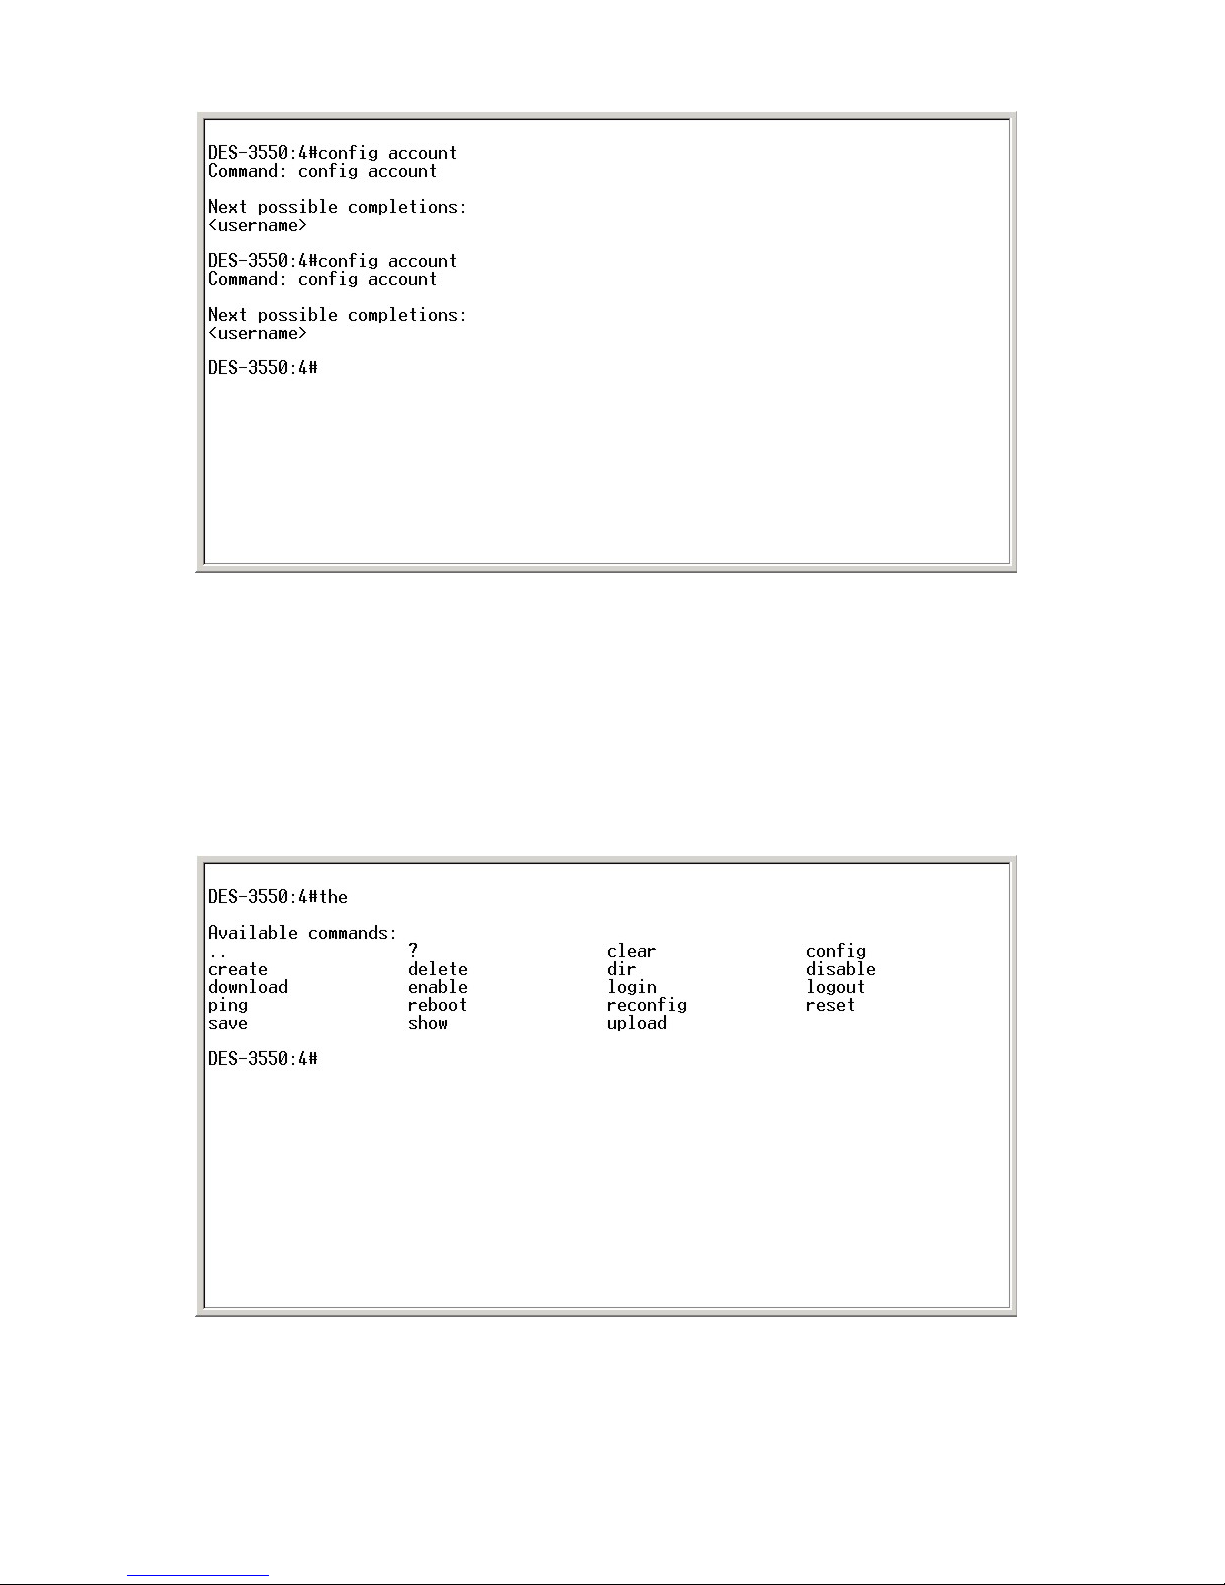
Figure 2-4. Using the Up Arrow to Re-enter a Command
In the above example, the command config account was entered without the required parameter <username>, the CLI returned
the Next possible completions: <username> prompt. The up arrow cursor control key was pressed to re-enter the previous
command (config account) at the command prompt. Now the appropriate username can be entered and the config account
command re-executed.
All commands in the CLI function in this way. In addition, the syntax of the help prompts are the same as presented in this
manual − angle brackets < > indicate a numerical value or character string, braces { } indicate optional parameters or a choice of
parameters, and brackets [ ] indicate required parameters.
If a command is entered that is unrecognized by the CLI, the top-level commands will be displayed under the
Available
commands: prompt.
Figure 2-5. The Next Available Commands Prompt
The top-level commands consist of commands such as show or config. Most of these commands require one or more parameters
to narrow the top-level command. This is equivalent to show what? or config what? Where the what? is the next parameter.
For example, if you enter the show command with no additional parameters, the CLI will then display all of the possible next
parameters.
6
Page 15
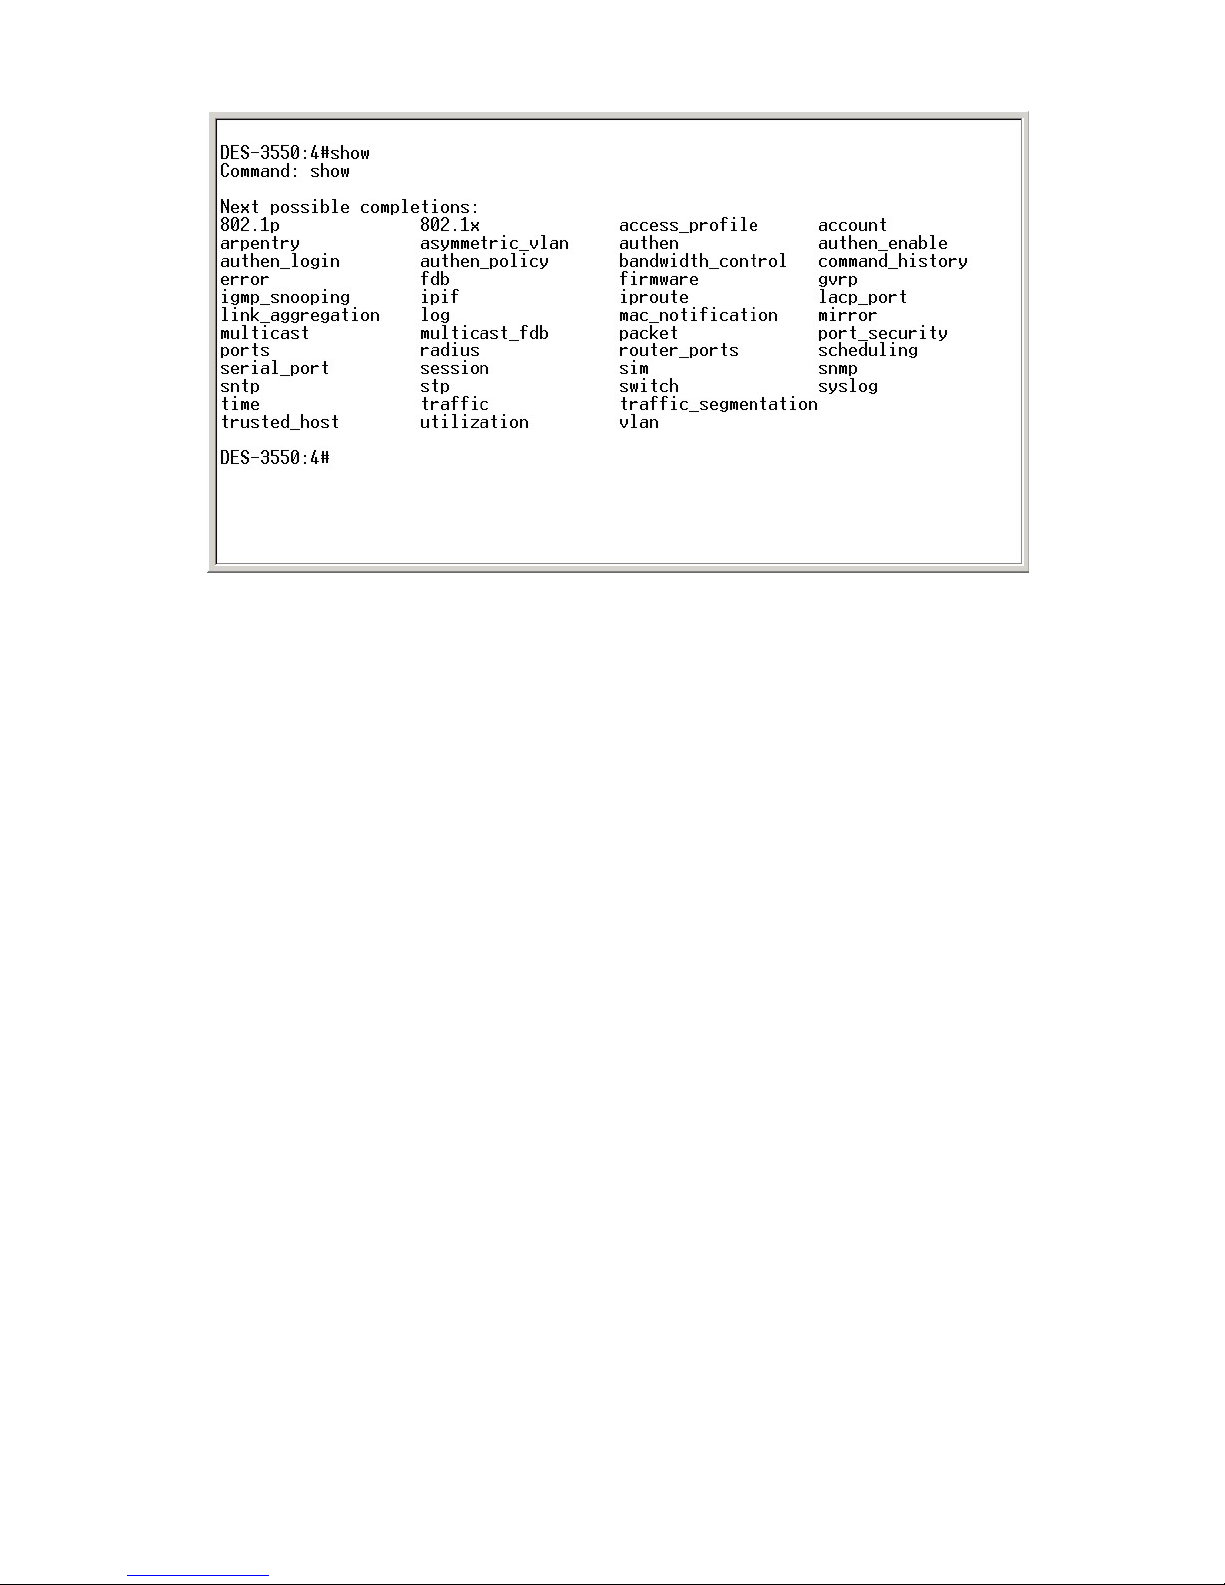
Figure 2-6. Next possible completions: Show Command
In the above example, all of the possible next parameters for the show command are displayed. At the next command prompt,
the up arrow was used to re-enter the show command, followed by the account parameter. The CLI then displays the user
accounts configured on the Switch.
7
Page 16
3
COMMAND SYNTAX
The following symbols are used to describe how command entries are made and values and arguments are specified in this
manual. The online help contained in the CLI and available through the console interface uses the same syntax.
Note: All commands are case-sensitive. Be sure to disable Caps Lock or any other
unwanted function that changes text case.
<angle brackets>
Purpose Encloses a variable or value that must be specified.
Syntax
Description In the above syntax example, you must supply an IP interface name in
Example
Command
create ipif <ipif_name> vlan <vlan_name 32> ipaddress
<network_address>
the <ipif_name> space, a VLAN name in the <vlan_name 32> space,
and the network address in the <network_address> space. Do not
type the angle brackets.
create ipif Engineering vlan Design ipaddress 10.24.22.5/255.0.0.0
[square brackets]
Purpose Encloses a required value or set of required arguments. One value or
argument can be specified.
Syntax
Description
Example
Command
create account [admin|user]
In the above syntax example, you must specify either an
level account to be created. Do not type the square brackets.
user
create account admin
admin
or a
| vertical bar
Purpose Separates two or more mutually exclusive items in a list, one of which
must be entered.
Syntax
Description
Example
Command
show snmp [community|detail]
In the above syntax example, you must specify either
detail
show snmp community
{braces}
Purpose Encloses an optional value or set of optional arguments.
Syntax
reset {[config|system]}
. Do not type the backslash.
8
community,
or
Page 17
{braces}
Description
Example
command
In the above syntax example, you have the option to specify
. It is not necessary to specify either optional value, however the
detail
effect of the system reset is dependent on which, if any, value is
specified. Therefore, with this example there are three possible
outcomes of performing a system reset. See the following chapter,
Basic Commands for more details about the reset command.
reset config
config
or
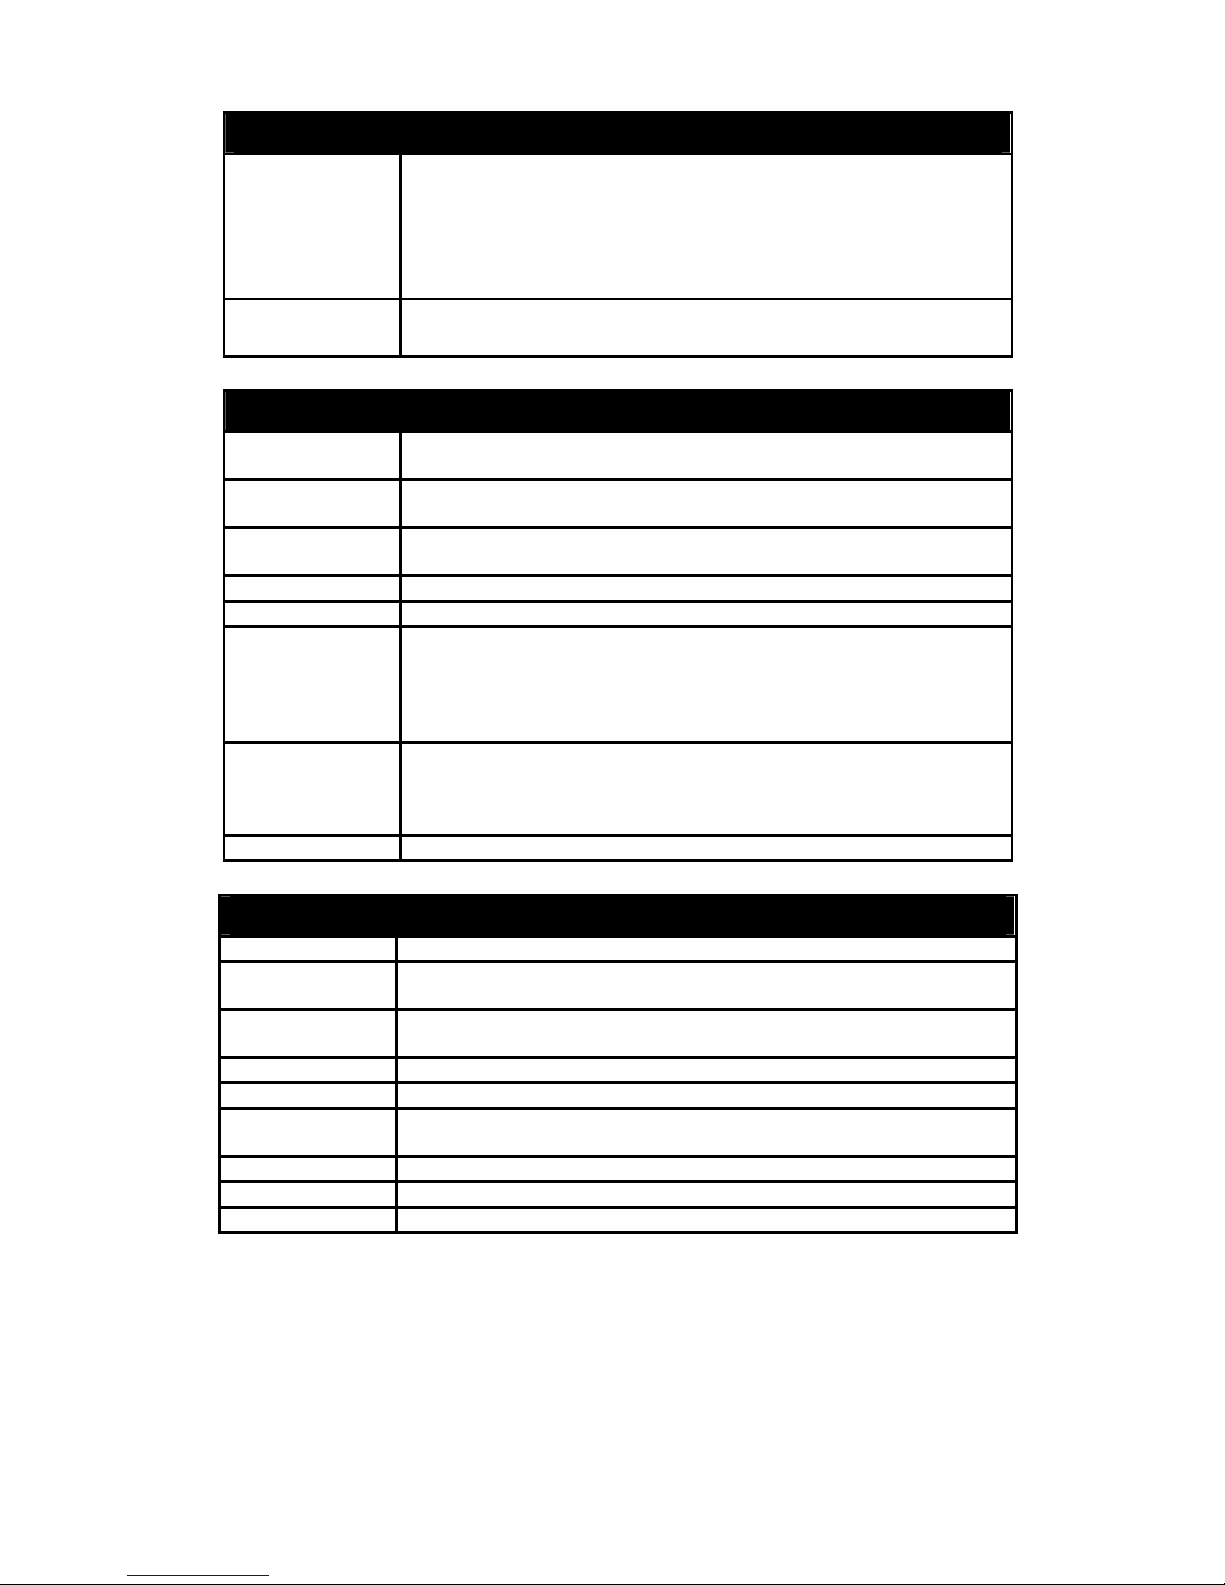
Line Editing Key Usage
Delete Deletes the character under the cursor and then shifts the remaining
characters in the line to the left.
Backspace Deletes the character to the left of the cursor and shifts the remaining
characters in the line to the left.
Insert or Ctrl+R Toggle on and off. When toggled on, inserts text and shifts previous
text to right.
Left Arrow Moves the cursor to the left.
Right Arrow Moves the cursor to the right.
Up Arrow Repeat the previously entered command. Each time the up arrow is
pressed, the command previous to that displayed appears. This way it
is possible to review the command history for the current session. Use
the down arrow to progress sequentially forward through the command
history list.
Down Arrow The down arrow will display the next command in the command history
entered in the current session. This displays each command
sequentially as it was entered. Use the up arrow to review previous
commands.
Tab Shifts the cursor to the next field to the left.
Multiple Page Display Control Keys
Space Displays the next page.
CTRL+c Stops the display of remaining pages when multiple pages are to be
displayed.
ESC Stops the display of remaining pages when multiple pages are to be
displayed.
n Displays the next page.
p Displays the previous page.
q Stops the display of remaining pages when multiple pages are to be
displayed.
r Refreshes the pages currently displayed.
a Displays the remaining pages without pausing between pages.
Enter Displays the next line or table entry.
9
Page 18
4
BASIC SWITCH COMMANDS
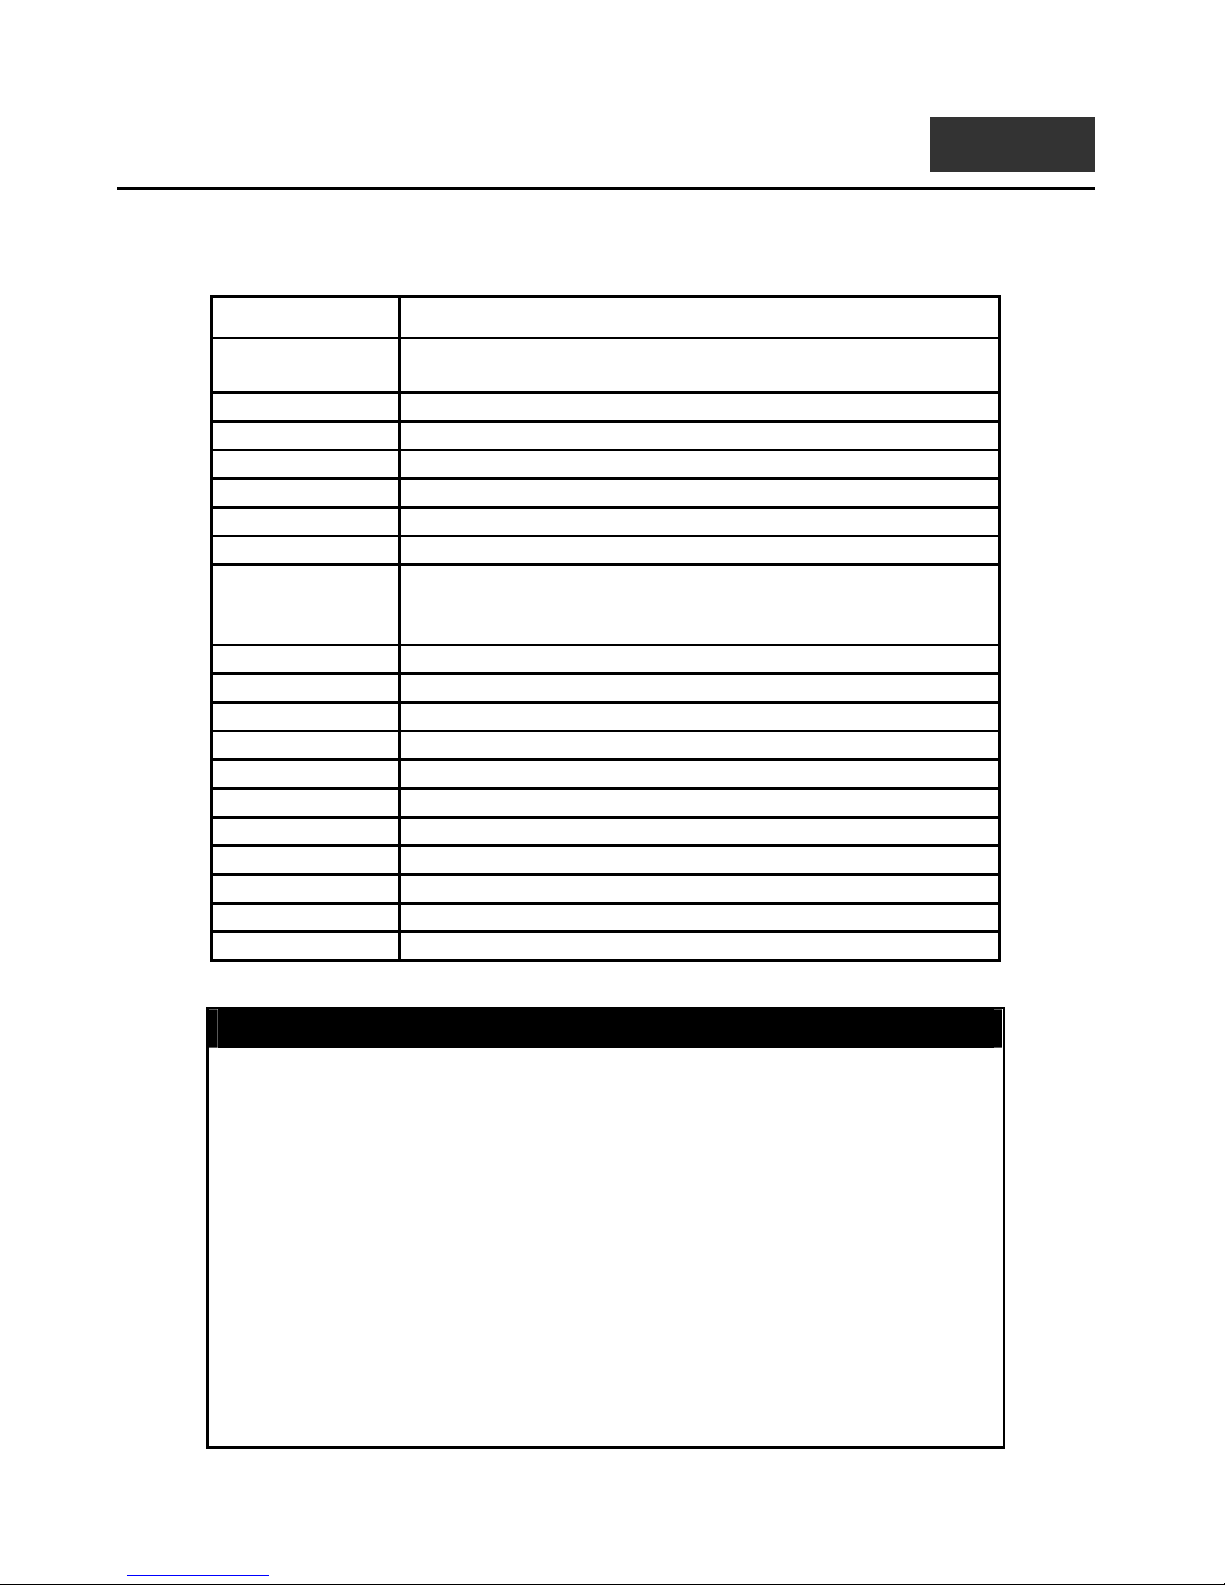
The basic switch commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in the
following table.
Command Parameters
create account [admin|user]
<username 15>
config account <username 15>
show account
delete account <username 15>
show session
show switch
show serial_port
config serial_port {baud_rate [9600|19200|38400|115200]
auto_logout [never|2_minutes|5_minutes
|10_minutes|15_minutes]}
enable clipaging
disable clipaging
enable telnet <tcp_port_number 1-65535>
disable telnet
enable web <tcp_port_number 1-65535>
disable web
save
reboot
reset {[config|system]}
login
logout
Each command is listed, in detail, in the following sections.
create account
Purpose
Syntax create [admin | user] <username 15>
Description
Parameters
Restrictions
Used to create user accounts
The create account command is used to create user accounts that
consist of a username of 1 to 15 characters and a password of 0 to 15
characters. Up to 8 user accounts can be created.
Admin <username>
User <username>
Only Administrator-level users can issue this command.
Usernames can be between 1 and 15 characters.
Passwords can be between 0 and 15 characters.
10
Page 19
Example usage:
To create an administrator-level user account with the username “dlink”.
DES-3550:4#create account admin dlink
Command: create account admin dlink
Enter a case-sensitive new password:****
Enter the new password again for confirmation:****
Success.
DES-3550:4#
config account
Example usage:
To configure the user password of “dlink” account:
Purpose
Syntax config account <username>
Description
Parameters
Restrictions
DES-3550:4#config account dlink
Command: config account dlink
Enter a old password:****
Enter a case-sensitive new password:****
Enter the new password again for confirmation:****
Success.
DES-3550:4#
Used to configure user accounts
The config account command configures a user account that has
been created using the
<username>
Only Administrator-level users can issue this command.
Usernames can be between 1 and 15 characters.
Passwords can be between 0 and 15 characters.
create account
command.
show account
Purpose
Syntax show account
Used to display user accounts
11
Page 20
show account
Example usage:
To display the accounts that have been created:
Description
Parameters
Restrictions
Displays all user accounts created on the switch. Up to 8 user
accounts can exist on the switch at one time.
None.
Only Administrator-level users can issue this command.
DES-3550:4#show account
Command: show account
Current Accounts:
Username Access Level
--------------- ------------
dlink Admin
Total Entries: 1
DES-3550:4#
Example usage:
To delete the user account “System”:
delete account
Purpose
Syntax delete account <username>
Description
Parameters
Restrictions
Used to delete an existing user account
The delete account command deletes a user account that has been
created using the
<username>
Only Administrator-level users can issue this command.
DES-3550:4#delete account System
Command: delete account System
Success.
DES-3550:4#
create account
command.
show session
Purpose
Used to display a list of currently logged-in users.
12
Page 21
show session
Syntax show session
Example usage:
To display the way that the users logged in:
Description
This command displays a list of all the users that are logged-in at
the time the command is issued.
Parameters
Restrictions
None
None.
DES-3550:4#show session
Command: show session
ID Login Time Live Time From Level Name
-- ------------------------------- --------- ------------ ----- -----------
*8 00000 days 00:00:37 03:36:27 Serial Port 4 Anonymous
show switch
Purpose
Used to display information about the switch.
Example usage:
To display the switch information:
Syntax show switch
Description
Parameters
Restrictions
DES-3550:4#show switch
Command: show switch
Device Type : DES-3550 Fast Ethernet Switch
Combo Port : 1000Base-T + 1000Base-T
MAC Address : 00-01-02-03-04-00
IP Address : 10.41.44.22 (Manual)
VLAN Name : default
Subnet Mask : 255.0.0.0
Default Gateway : 0.0.0.0
Boot PROM Version : Build 3.00.001
Firmware Version : Build 1.00-B02
Hardware Version : 2A1
Device S/N :
Power Status : Main – Normal, Redundant – Not Present
System Name : DES-3550
This command displays information about the switch.
None.
Only Administrator-level users can issue this command.
13
Page 22
System Location : 7th_flr_east_cabinet
System Contact : Julius_Erving_212-555-6666
Spanning Tree : Disabled
GVRP : Disabled
IGMP Snooping : Disabled
TELNET : Enabled (TCP 23)
WEB : Enabled (TCP 80)
RMON : Enabled
Asymmetric VLAN : Disabled
DES-3550:4#
show serial_port
Purpose
Syntax show serial_port
Description
Parameters
Restrictions
Example usage:
To display the serial port setting:
Used to display the current serial port settings.
This command displays the current serial port settings.
None.
None
DES-3550:4#show serial_port
Command: show serial_port
Baud Rate : 9600
Data Bits : 8
Parity Bits : None
Stop Bits : 1
Auto-Logout : 10 mins
DES-3550:4#
config serial_port
Purpose
Syntax config serial_port {baud_rate [9600|19200|38400|115200] |
Description
Parameters
Used to configure the serial port and the auto logout time for idle
connections.
auto_logout [never | 2_minutes | 5_minutes | 10_minutes |
15_minutes]}
This command is used to configure the serial port’s baud rate and auto
logout settings.
baud_rate[9600|19200|38400|115200]− The serial bit rate that will be used
to communicate with the management host. There are four options: 9600,
14
Page 23
config serial_port
19200, 38400, 115200.
never − No time limit on the length of time the console can be open with no
user input.
2_minutes − The console will log out the current user if there is no user
input for 2 minutes.
5_minutes − The console will log out the current user if there is no user
input for 5 minutes.
10_minutes − The console will log out the current user if there is no user
input for 10 minutes.
15_minutes − The console will log out the current user if there is no user
input for 15 minutes.
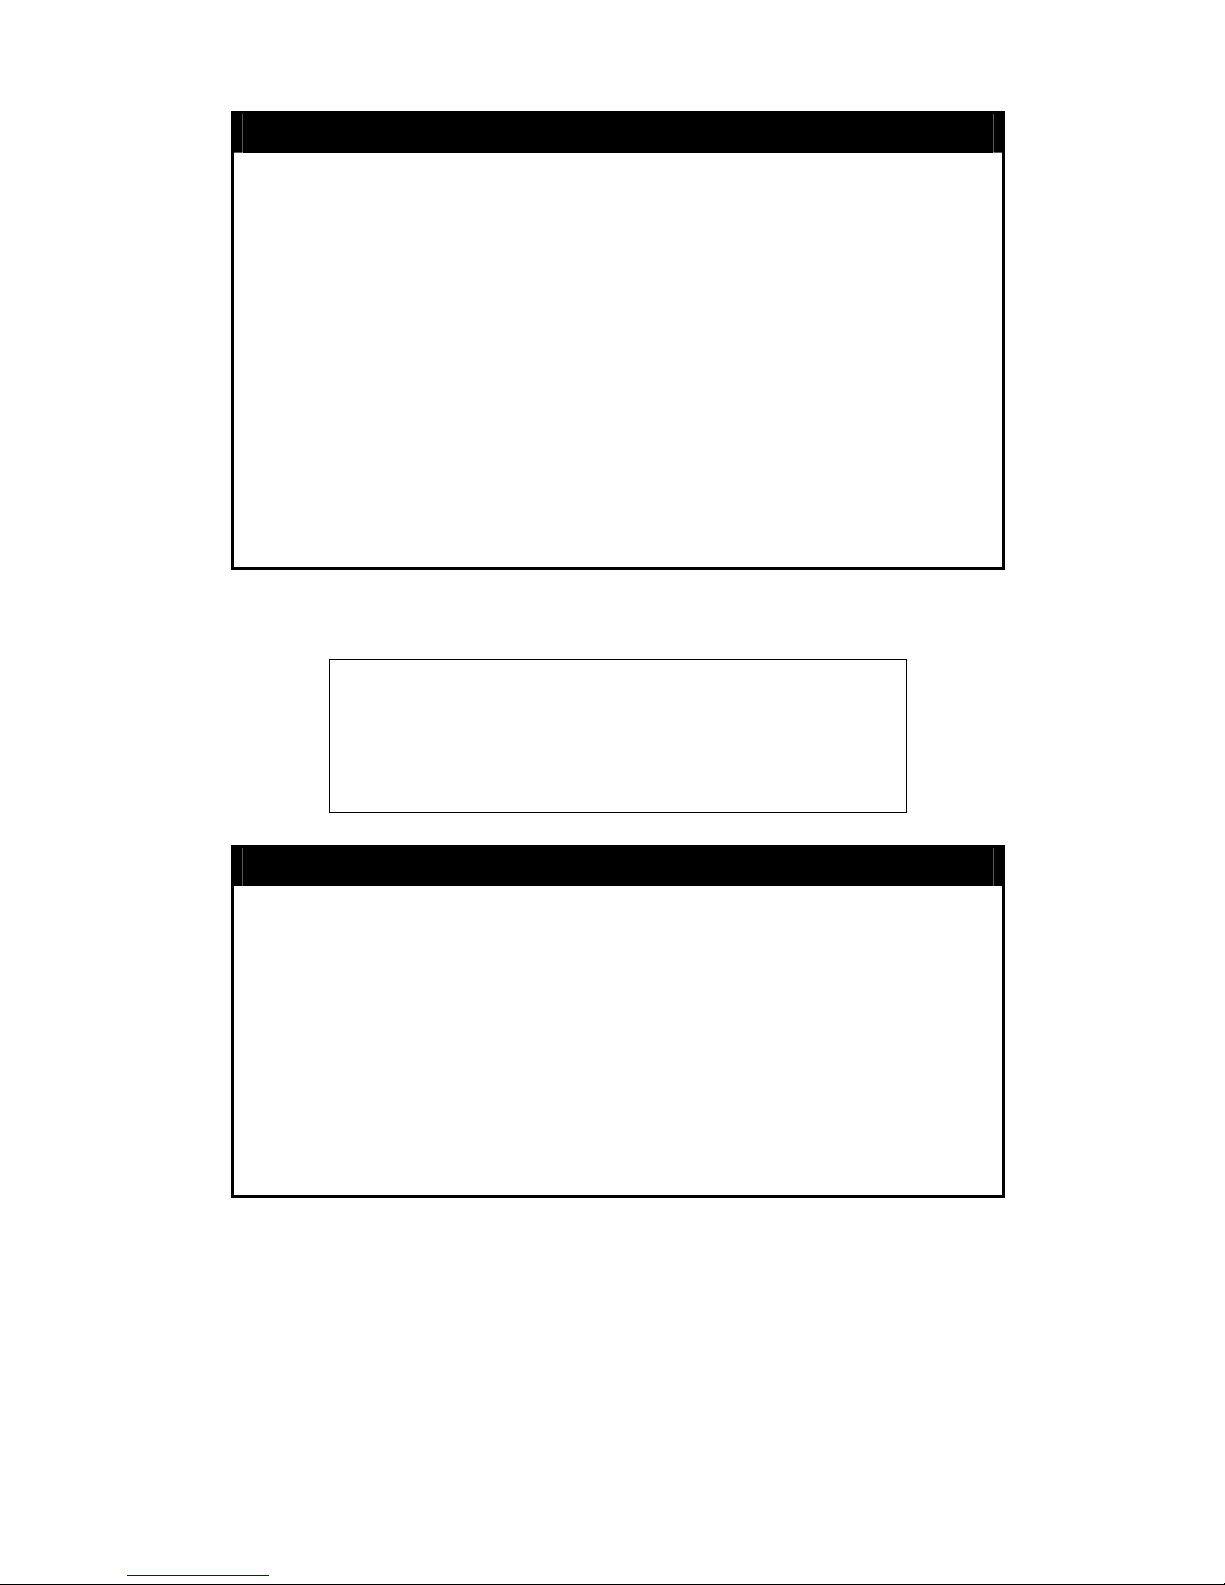
Example usage:
To configure baud rate:
Restrictions
Only administrator-level users can issue this command.
DES-3550:4#config serial_port baud_rate 115200
Command: config serial_port baud_rate 115200
Success.
DES-3550:4#
enable clipaging
Purpose
Syntax enable clipaging
Description
Used to pause the scrolling of the console screen when the show
command displays more than one page.
This command is used when issuing the show command which
causes the console screen to rapidly scroll through several pages.
This command will cause the console to pause at the end of each
page. The default setting is enabled.
Parameters
Restrictions
Example usage:
To enable pausing of the screen display when the show command output reaches the end of the page:
None.
Only administrator-level users can issue this command.
15
Page 24
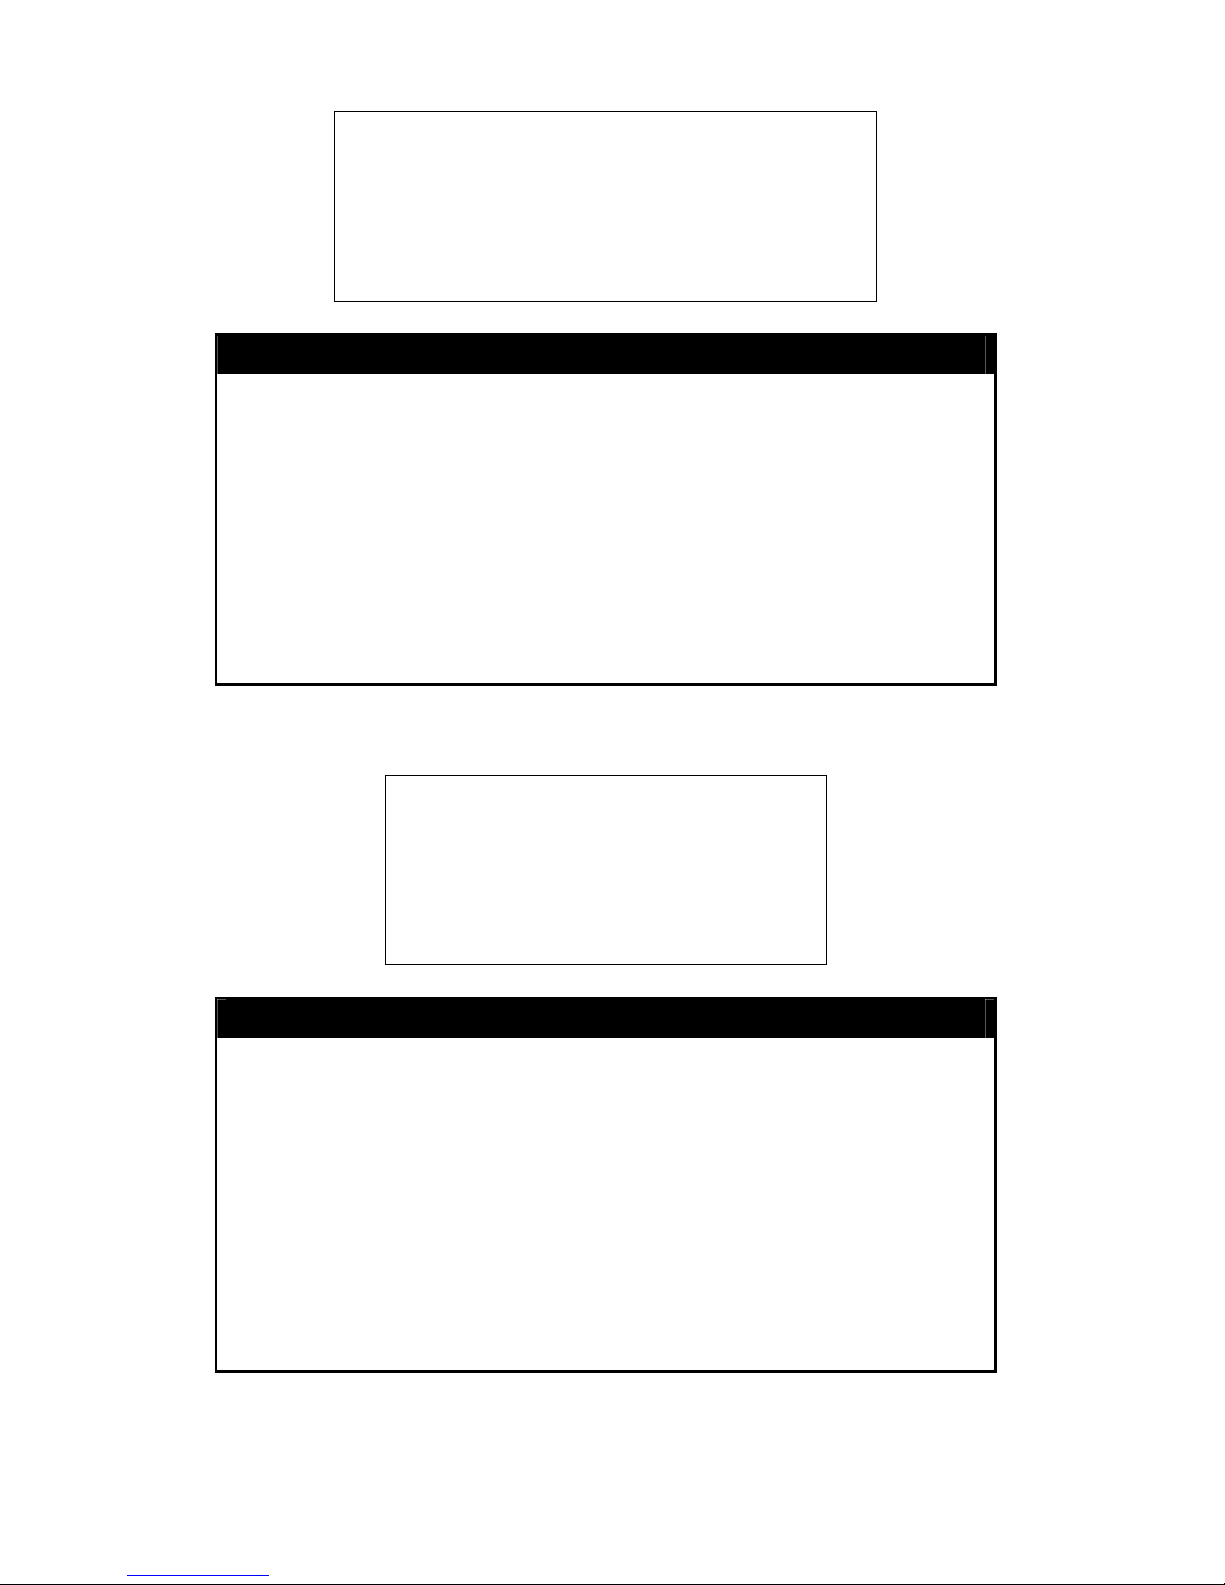
DES-3550:4#enable clipaging
Command: enable clipaging
Success.
DES-3550:4#
disable clipaging
Purpose
Syntax disable clipaging
Description
Parameters
Restrictions
Example usage:
To disable pausing of the screen display when show command output reaches the end of the page:
Used to disable the pausing of the console screen scrolling at the end
of each page when the show command displays more than one
screen of information.
This command is used to disable the pausing of the console screen
at the end of each page when the show command would display
more than one screen of information.
None.
Only administrator-level users can issue this command.
DES-3550:4#disable clipaging
Command: disable clipaging
Success.
DES-3550:4#
enable telnet
Purpose
Syntax enable telnet <tcp_port_number 1-65535>
Description
Parameters
Restrictions
Example usage:
To enable Telnet and configure port number:
Used to enable communication with and management of the switch
using the Telnet protocol.
This command is used to enable the Telnet protocol on the switch.
The user can specify the TCP or UDP port number the switch will use
to listen for Telnet requests.
<tcp_port_number> − The TCP port number. TCP ports are
numbered between 1 and 65535. The “well-known” TCP port for the
Telnet protocol is 23.
Only administrator-level users can issue this command.
16
Page 25
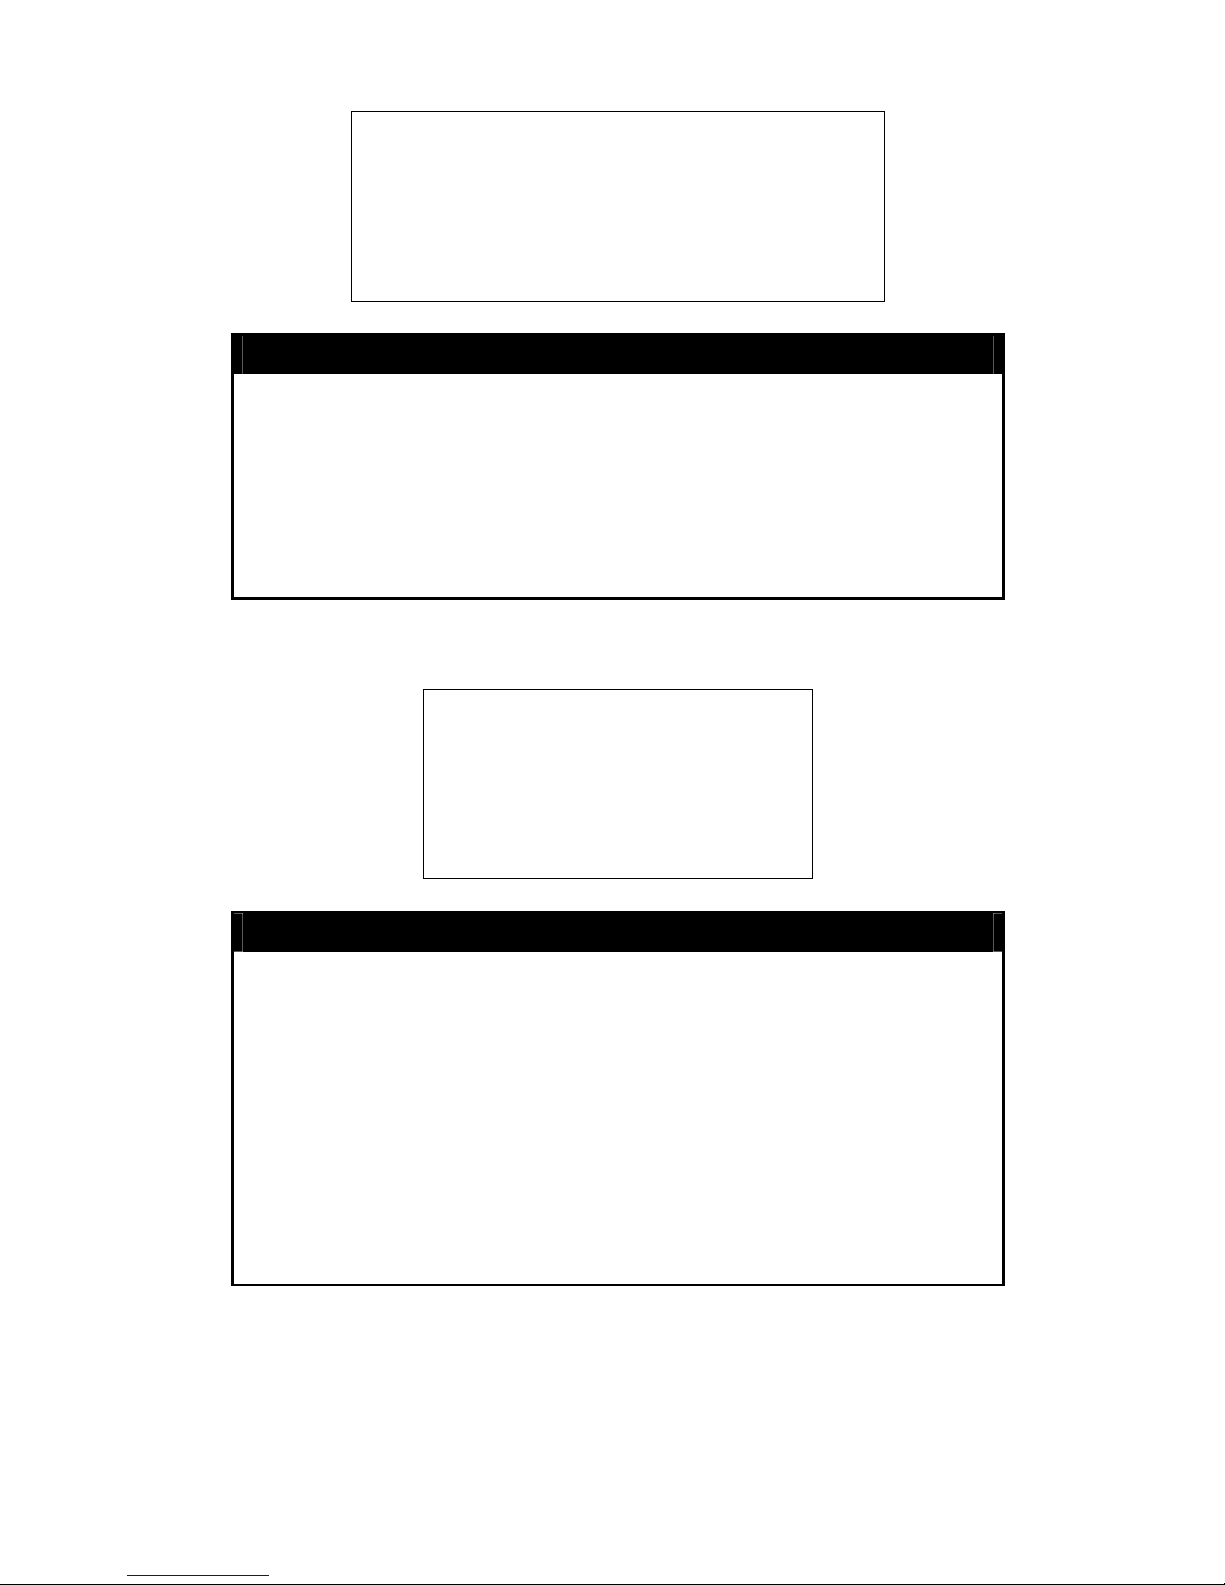
DES-3550:4#enable telnet 23
Command: enable telnet 23
Success.
DES-3550:4#
disable telnet
Example usage:
To disable the Telnet protocol on the switch:
Purpose
Syntax disable telnet
Description
Parameters
Restrictions
Used to disable the Telnet protocol on the switch.
This command is used to disable the Telnet protocol on the switch.
None.
Only administrator-level users can issue this command.
DES-3550:4#disable telnet
Command: disable telnet
Success.
DES-3550:4#
enable web
Purpose
Used to enable the HTTP-based management software on the
switch.
Syntax enable web <tcp_port_number 1-65535>
Description
Parameters
Restrictions
Example usage:
To enable HTTP and configure port number:
This command is used to enable the Web-based management
software on the switch. The user can specify the TCP port number
the switch will use to listen for Telnet requests.
<tcp_port_number> − The TCP port number. TCP ports are
numbered between 1 and 65535. The “well-known” port for the Webbased management software is 80.
Only administrator-level users can issue this command.
17
Page 26
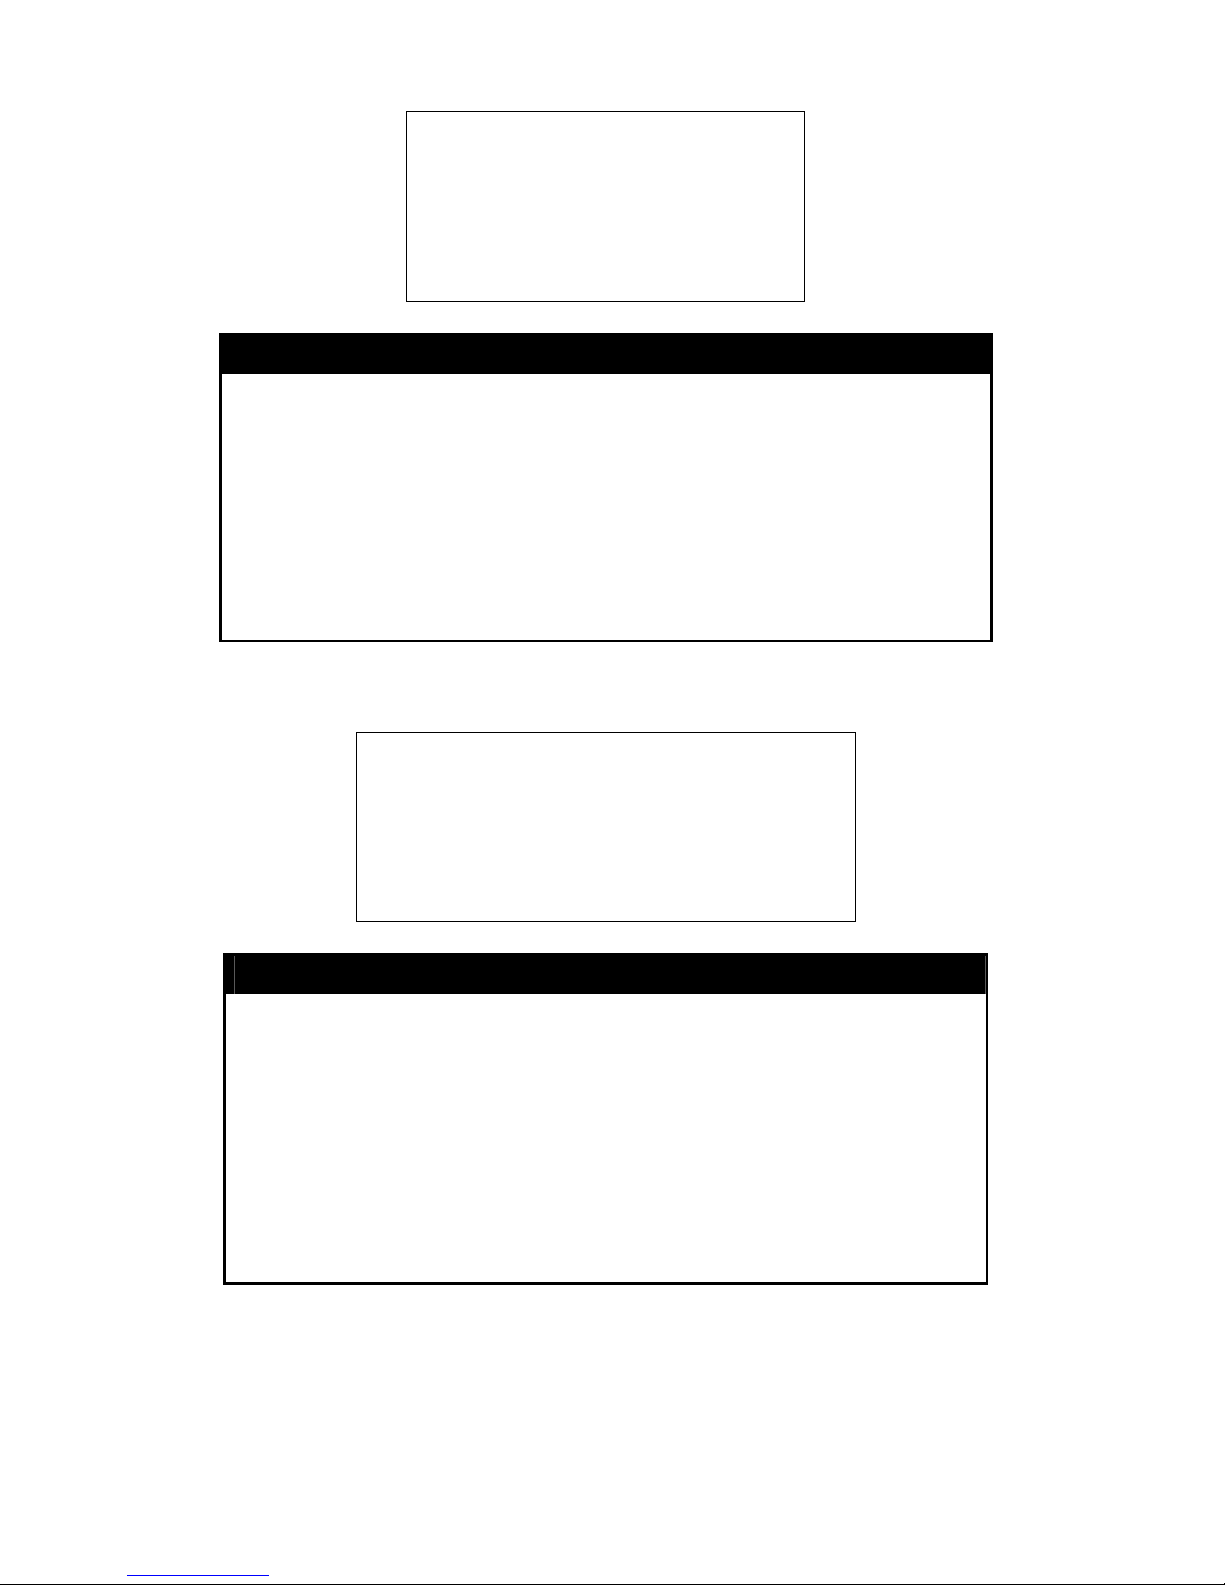
DES-3550:4#enable web 80
Command: enable web 80
Success.
DES-3550:4#
disable web
Example usage:
To disable HTTP:
Purpose
Syntax disable web
Description
Parameters
Restrictions
Used to disable the HTTP-based management software on the
switch.
This command disables the Web-based management software on
the switch.
None.
Only administrator-level users can issue this command.
DES-3550:4#disable web
Command: disable web
Success.
DES-3550:4#
Example usage:
To save the switch’s current configuration to non-volatile RAM:
save
Purpose
Syntax save
Description
Parameters
Restrictions
Used to save changes in the switch’s configuration to non-volatile
RAM.
This command is used to enter the current switch configuration into
non-volatile RAM. The saved switch configuration will be loaded
into the switch’s memory each time the switch is restarted.
None
Only administrator-level users can issue this command.
18
Page 27
DES-3550:4#save
Command: save
Saving all configurations to NV-RAM... Done.
DES-3550:4#
reboot
Purpose
Syntax reboot
Description
Parameters
Restrictions
Example usage:
To restart the switch:
DES-3550:4#reboot
Command: reboot
Are you sure want to proceed with the system reboot? (y|n)
Please wait, the switch is rebooting...
reset
Purpose
Syntax reset {[config|system]}
Used to restart the switch.
This command is used to restart the switch.
None.
None.
Used to reset the switch to the factory default settings.
Description
Parameters
Restrictions
Example usage:
This command is used to restore the switch’s configuration to the
default settings assigned from the factory.
config − If the keyword ‘config’ is specified, all of the factory default
settings are restored on the switch including the IP address, user
accounts, and the switch history log. The switch will not save or
reboot.
system − If the keyword ‘system’ is specified all of the factory default
settings are restored on the switch. The switch will save and reboot
after the settings are changed to default. Rebooting will clear all
entries in the Forwarding Data Base.
If no parameter is specified, the switch’s current IP address, user
accounts, and the switch history log are not changed. All other
parameters are restored to the factory default settings. The switch
will not save or reboot.
Only administrator-level users can issue this command.
19
Page 28
To restore all of the switch’s parameters to their default values:
DES-3550:4#reset config
Command: reset config
Are you sure to proceed with system reset?(y/n)
Success.
DES-3550:4#
login
Example usage:
To initiate the login procedure:
Purpose
Syntax login
Description
Parameters
Restrictions
DES-3550:4#login
Command: login
UserName:
Used to log in a user to the switch’s console.
This command is used to initiate the login procedure. The user will
be prompted for his Username and Password.
None.
None.
logout
Purpose
Used to log out a user from the switch’s console.
Syntax logout
Description
Parameters
Restrictions
Example usage:
To terminate the current user’s console session:
DES-3550:4#logout
This command terminates the current user’s session on the
switch’s console.
None.
None.
20
Page 29
5
SWITCH PORT COMMANDS
The switch port commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in the
following table.
Command Parameters
config ports [<portlist | all> {speed [auto | 10_half | 10_full |100_half | 100_full |
1000_full} | flow_control [enable | disable] | learning [enable |
disable] state [enable | disable]} description <desc 32>
show ports <portlist> {description}
Each command is listed, in detail, in the following sections.
config ports
Purpose
Syntax config ports [<portlist | all>] {speed [auto | 10_half | 10_full |100_half
Description
Parameters
Used to configure the Switch’s Ethernet port settings.
| 100_full | 1000_half | 1000_full} | flow_control [enable | disable] |
learning [enable | disable] state [enable | disable] description <desc
32>
This command allows for the configuration of the switch’s Ethernet ports.
Only the ports listed in the <portlist> will be affected.
all − Configure all ports on the switch.
<portlist> − Specifies a port or range of ports to be configured. Tauto −
Enables auto-negotiation for the specified range of ports.
[10|100|1000] − Configures the speed in Mbps for the specified range of
ports. Gigabit ports are statically set to 1000 and cannot be set to slower
speeds.
[half|full] − Configures the specified range of ports as either full- or halfduplex.
[master | slave] This parameter denotes whether the ports selected will be
of the master switch or the slave switch and is only used when the port
speed is selected to be 1000_full.
flow_control [enabled | disabled] – Enable or disable flow control for the
specified ports.
learning [enabled | disabled] − Enables or disables the MAC address
learning on the specified range of ports.
state [enabled | disabled] − Enables or disables the specified range of
ports.
description <desc 32> - Enter an alphanumeric string of no more than 32
characters to describe a selected port interface.
Restrictions
Example usage:
Only administrator-level users can issue this command.
21
Page 30
To configure the speed of port 3 to be 10 Mbps, full duplex, with learning and state enabled:
DES-3550:4#config ports 1-3 speed 10_full learning enabled
state enabled
Command: config ports 1-3 speed 10_full learning enabled
state enabled
Success.
DES-3550:4#
show ports
Example usage:
To display the configuration of all ports on a switch:
Purpose
Used to display the current configuration of a range of ports.
Syntax show ports <portlist> {description}
Description
This command is used to display the current configuration of a range
of ports.
Parameters
<portlist> − Specifies a port or range of ports to be displayed.
{description} – Adding this parameter to the
indicates that the port description will be included in the display.
Restrictions
None.
DES-3550:4#show ports
Command show ports:
Port Port Settings Connection Address
State Speed/Duplex/FlowCtrl Speed/Duplex/FlowCtrl Learning
------ -------- --------------------- --------------------- -------1 Enabled Auto/Enabled Link Down Enabled
2 Enabled Auto/Enabled Link Down Enabled
3 Enabled Auto/Enabled Link Down Enabled
4 Enabled Auto/Enabled Link Down Enabled
5 Enabled Auto/Enabled Link Down Enabled
6 Enabled Auto/Enabled Link Down Enabled
7 Enabled Auto/Enabled Link Down Enabled
8 Enabled Auto/Enabled Link Down Enabled
9 Enabled Auto/Enabled Link Down Enabled
10 Enabled Auto/Enabled 100M/Full/None Enabled
11 Enabled Auto/Enabled Link Down Enabled
12 Enabled Auto/Enabled Link Down Enabled
13 Enabled Auto/Disabled Link Down Enabled
14 Enabled Auto/Disabled Link Down Enabled
15 Enabled Auto/Disabled Link Down Enabled
16 Enabled Auto/Disabled Link Down Enabled
17 Enabled Auto/Disabled Link Down Enabled
18 Enabled Auto/Disabled Link Down Enabled
19 Enabled Auto/Disabled Link Down Enabled
20 Enabled Auto/Disabled Link Down Enabled
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
show ports
command
22
Page 31
Example usage:
To display the configuration of all ports on a switch, with description:
DES-3550:4#show ports description
Command: show ports description
Port Port Settings Connection Address
State Speed/Duplex/FlowCtrl Speed/Duplex/FlowCtrl Learning
------ -------- --------------------- --------------------- --------
1 Enabled Auto/Disabled Link Down Enabled
Description: dads1
2 Enabled Auto/Disabled Link Down Enabled
Description:
3 Enabled Auto/Disabled Link Down Enabled
Description:
4 Enabled Auto/Disabled Link Down Enabled
Description:
5 Enabled Auto/Disabled Link Down Enabled
Description:
6 Enabled Auto/Disabled Link Down Enabled
Description:
7 Enabled Auto/Disabled Link Down Enabled
Description:
8 Enabled Auto/Disabled Link Down Enabled
Description:
9 Enabled Auto/Disabled Link Down Enabled
Description:
10 Enabled Auto/Disabled Link Down Enabled
Description:
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
23
Page 32
6
PORT SECURITY COMMANDS
The switch port security commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in
the following table.
Command Parameters
config port_security
ports
delete port_security
entry
clear
port_security_entry
show port_security {ports <portlist>}
Each command is listed, in detail, in the following sections.
[<portlist>| all ] {admin_state [enable| disable]
|max_learning_addr <max_lock_no 0-10> | lock_address_mode
[Permanent | DeleteOnTimeout | DeleteOnReset]}
vlan_name <vlan_name 32> mac_address <macaddr> port <port>
port <portlist>
config port_security ports
Purpose
Syntax config port_security ports [<portlist>| all ] {admin_state [enable|
Description
Parameters
Used to configure port security settings.
disable] | max_learning_addr <max_lock_no 0-10> |
lock_address_mode [Permanent | DeleteOnTimeout |
DeleteOnReset]}
This command allows for the configuration of the port security feature.
Only the ports listed in the <portlist> are effected.
portlist − specifies a port or range of ports to be configured.
Example usage:
Restrictions
all − configure port security for all ports on the switch.
admin_state [enable|disable] – enable or disable port security for the listed
ports.
max_learning_addr <max_lock_no 0-10> - use this to limit the number of
MAC addresses dynamically listed in the FDB for the ports.
lock_address_mode[Permanent | DeleteOnTimout | DeleteOnReset] –
Indicates the method of locking addresses. The user has three choices:
Permanent – The locked addresses will not age out after the
aging timer expires.
DeleteOnTimeout – The locked addresses will age out after the
aging timer expires.
DeleteOnReset – The locked addresses will not age out until the
switch has been reset.
Only administrator-level users can issue this command.
24
Page 33
To configure the port security:
DES-3550:4#config port_security ports 1-5 admin_state enable
max_learning_addr 5 lock_address_mode DeleteOnReset
Command: config port_security ports 1-5 admin_state enable
max_learning_addr 5 lock_address_mode DeleteOnReset
Success.
DES-3550:4#
delete port_security_entry
Purpose
Syntax delete port_security_entry vlan name <vlan_name 32>
Description
Parameters
Restrictions
Example usage:
To delete a port security entry:
DES-3550:4#delete port_security_entry vlan_name default
mac_address 00-01-30-10-2C-C7 port 6
Command: delete port_security_entry vlan_name default
mac_address 00-01-30-10-2C-C7 port 6
Success.
DES-3550:4#
Used to delete a port security entry by MAC address, port number
and VLAN ID.
mac_address <macaddr> port <port>
This command is used to delete a single, previously learned port
security entry by port, VLAN name, and MAC Address.
vlan name <vlan_name 32> Enter the corresponding vlan name of
the port which the user wishes to delete.
mac_address <macaddr> - Enter the corresponding MAC address,
previously learned by the port, which the user wishes to delete.
port <port> - Enter the port number which has learned the previously
enterd MAC address.
Only administrator-level users can issue this command.
clear port_security_entry
Purpose
Syntax clear port_security_entry port <portlist>
Description
Used to clear MAC address entries learned from a specified port for
the port security function.
This command is used to clear MAC address entries which were
learned by the switch by a specified port. This command only relates
25
Page 34
clear port_security_entry
to the port security function.
Parameters
Restrictions
Example usage:
To clear a port security entry by port:
DES-3550:4# clear port_security_entry port 6
Command: clear port_security_entry port 6
Success.
DES-3550:4#
<portlist> − specifies a port or port range the user wishes to clear.
Only administrator-level users can issue this command.
show port_security
Purpose
Syntax show port_security {ports <portlist>}
Description
Used to display the current port security configuration.
This command is used to display port security information of the
switch ports. The information displayed includes port security admin
state, maximum number of learning address and lock mode.
Example usage:
To display the port security configuration:
Parameters
Restrictions
DES-3550:4#show port_security ports 1-5
Command: show port_security ports 1-5
Port# Admin State Max. Learning Addr. Lock Address Mode
---- ----------- ------------------- ---------------- 1 Disabled 1 DeleteOnReset
2 Disabled 1 DeleteOnReset
3 Disabled 1 DeleteOnReset
4 Disabled 1 DeleteOnReset
5 Disabled 1 DeleteOnReset
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
<portlist> − specifies a port or range of ports to be viewed.
None.
26
Page 35
7
NETWORK MANAGEMENT (SNMP) COMMANDS
The network management commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in
the following table.
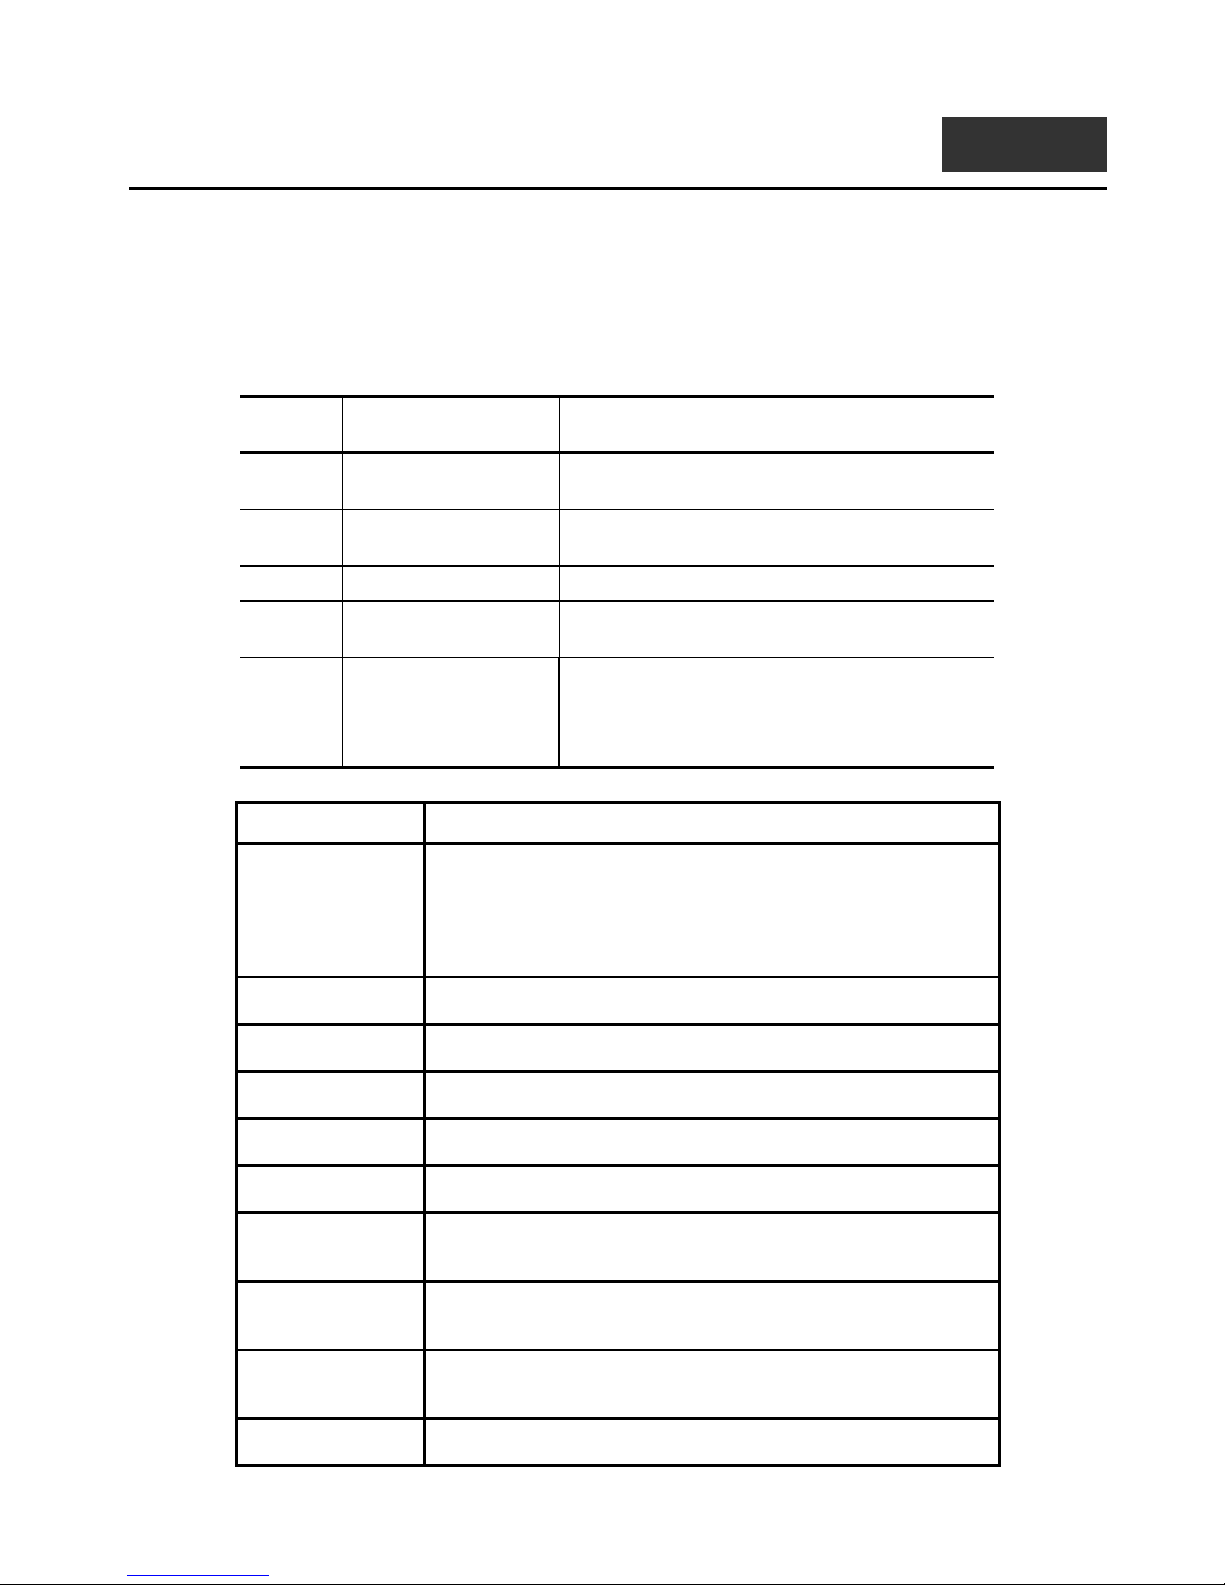
The DES-3550 supports the Simple Network Management Protocol (SNMP) versions 1, 2c, and 3. You can specify which
version of the SNMP you want to use to monitor and control the switch. The three versions of SNMP vary in the level of
security provided between the management station and the network device. The following table lists the security features of the
three SNMP versions:
SNMP
Version
v1 Community String
v2c Community String
v3 Username
v3 MD5 or SHA Authentication is based on the HMAC-MD5 or
v3 MD5 DES or SHA DES Authentication is based on the HMAC-MD5 or
Authentication Method Description
Community String is used for authentication −
NoAuthNoPriv
Community String is used for authentication −
NoAuthNoPriv
Username is used for authentication − NoAuthNoPriv
HMAC-SHA algorithms − AuthNoPriv
HMAC-SHA algorithms − AuthPriv.
DES 56-bit encryption is added based on the CBC-
DES (DES-56) standard
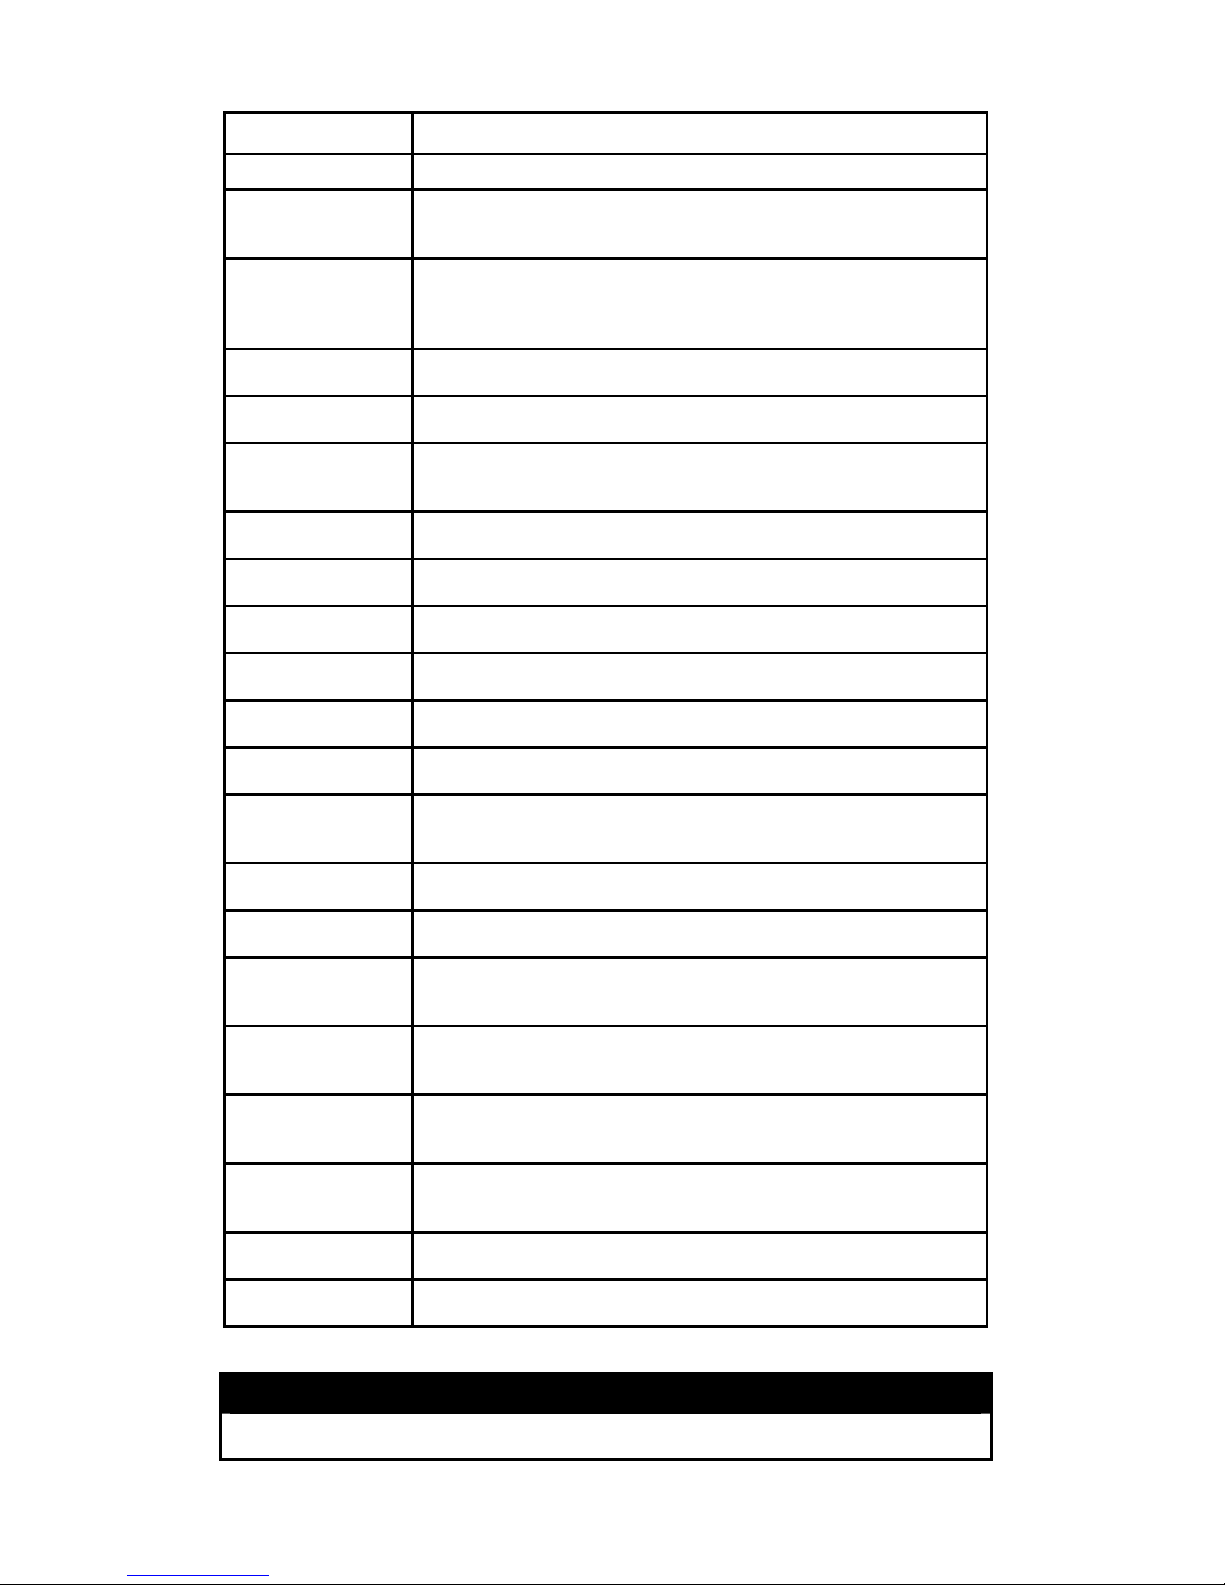
Command Parameters
create snmp user <username 32> <groupname 32> {encrypted [by_password auth
[md5 <auth_password 8-16 > | sha <auth_password 8-20 >] priv
[none | des <priv_password 8-16> ] | by_key auth [md5 <auth_key
32-32>| sha <auth_key 40-40>] priv [none | des <priv_key 3232> ]]}
delete snmp user <SNMP_name 32>
show snmp user
create snmp view
delete snmp view <view_name 32> [all | oid]
show snmp view <view_name 32>
create snmp
community
delete snmp
community
show snmp
community
config snmp
<view_name 32> <oid> view_type [included | excluded]
<community_string 32> view <view_name 32> [read_only |
read_write]
<community_string 32>
<community_string 32>
<snmp_engineID>
27
Page 36
Command Parameters
engineID
show snmp
engineID
create snmp group <groupname 32> {v1 | v2c |v3 [noauth_nopriv | auth_nopriv |
delete snmp group <groupname 32>
show snmp groups
create snmp host <ipaddr> {v1 |v2c | v3 [noauth_nopriv | auth_nopriv | auth_priv]}
delete snmp host <ipaddr>
show snmp host <ipaddr>
create trusted_host <ipaddr>
delete trusted_host <ipaddr>
show trusted_host <ipaddr>
enable snmp traps
auth_priv ]} {read_view <view_name 32> | write_view
<view_name 32> | notify_view <view_name 32>}
<auth_string 32>
enable snmp
authenticate_traps
show snmp traps
disable snmp traps
disable snmp
authenticate_traps
config snmp system
contact
config snmp system
location
config snmp system
name
enable rmon
disable rmon
Each command is listed, in detail, in the following sections.
<sw_contact>
<sw_location>
<sw_name>
create snmp user
Purpose Used to create a new SNMP user and adds the user to an SNMP
28
Page 37
create snmp user
group that is also created by this command.
Syntax
Description
Parameters
create snmp user <username 32> <groupname 32> {encrypted
[by_password auth [md5 <auth_password 8-16 > | sha
<auth_password 8-20 >] priv [none | des <priv_password 816> ]|by_key auth [md5 <auth_key 32-32>| sha <auth_key 4040>] priv [none | des <priv_key 32-32> ]]}
The
create snmp user
adds the user to an SNMP group that is also created by this
command.
<username 32> − An alphanumeric name of up to 32 characters that
will identify the new SNMP user.
<groupname 32> − An alphanumeric name of up to 32 characters
that will identify the SNMP group the new SNMP user will be
associated with.
by_password – Requires the SNMP user to enter a password for
authentication and privacy. The password is defined by specifying
the auth_password below. This method is recommended.
by_key - Requires the SNMP user to enter a encryption key for
authentication and privacy. The key is defined by specifying the
priv_password below. This method is not recommended.
Message integrity − ensures that packets have not been tampered
with during transit.
command creates a new SNMP user and
Authentication − determines if an SNMP message is from a valid
source.
Encryption − scrambles the contents of messages to prevent it being
viewed by an unauthorized source.
encrypted – Specifies that the password will be in an encrypted
format.
auth [md5|sha] – Initiate an authentication-level setting session.
− Specifies that the HMAC-MD5-96 authentication level will be
md5
used.
− Specifies that the HMAC-SHA-96 authentication level will be
sha
used.
<auth_password 8-20> − An alphanumeric sting of between 8 and
20 characters that will be used to authorize the agent to receive
packets for the host.
des <priv_password 8-16> − An alphanumeric string of between 8
and 16 characters that will be used to encrypt the contents of
messages the host sends to the agent.
Restrictions Only administrator-level users can issue this command.
Example usage:
29
Page 38
To create an SNMP user on the switch:
DES-3550:4#create snmp user dlink default encrypted
by_password auth md5 auth_password priv none
Command: create snmp user dlink default encrypted
by_password auth md5 auth_password priv none
Success.
DES-3550:4#
delete snmp user
Example usage:
To delete a previously entered SNMP user on the switch:
Purpose
Syntax delete snmp user <usmusername 32>
Description
Parameters
Restrictions
Used to remove an SNMP user from an SNMP group and also to
delete an entry from the USM User Table Settings
The
delete snmp user
SNMP group and then deletes the entry from the USM User Table
Settings.
<username 32> − An alphanumeric string of up to 32 characters that
identifies the SNMP user that will be deleted.
Only administrator-level users can issue this command.
DES-3550:4#delete snmp user dlink
Command: delete snmp user dlink
Success.
DES-3550:4#
command removes an SNMP user from its
show snmp user
Purpose Used to display information about each SNMP username in the
SNMP group username table.
Syntax
Description
Parameters None.
Restrictions Only administrator-level users can issue this command.
Example usage:
To display the SNMP users currently configured on the switch:
show snmp user
The
SNMP username in the SNMP group username table.
show snmp user
command displays information about each
30
Page 39
DES-3550:4#show snmp user
Command: show snmp user
Username Group Name Ver Auth Priv
--------------- -------------- ----- -------- -------
initial initial V3 None None
Total Entries: 1
DES-3550:4#
create snmp view
Purpose Used to assign views to community strings to limit which MIB objects
and SNMP manager can access.
Example usage:
To create an SNMP view:
Syntax
Description The
Parameters <view_name 32> − An alphanumeric string of up to 32 characters
Restrictions Only administrator-level users can issue this command.
DES-3550:4#create snmp view dlinkview 1.3.6 view_type
included
Command: create snmp view dlinkview 1.3.6 view_type included
Success.
DES-3550:4#
create snmp view <view_name 32> <oid> view_type [included |
excluded]
create snmp view
strings to limit which MIB objects an SNMP manager can access.
that identifies the SNMP view that will be created.
<oid> − The object ID that identifies an object tree (MIB tree) that will
be included or excluded from access by an SNMP manager.
included − Include this object in the list of objects that an SNMP
manager can access.
excluded − Exclude this object from the list of objects that an SNMP
manager can access.
command assigns views to community
delete snmp view
Purpose Used to remove an SNMP view entry previously created on the
switch.
31
Page 40
delete snmp view
Example usage:
To delete a previously configured SNMP view from the switch:
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
delete snmp view <view_name 32> [all | <oid>]
The
delete snmp view
previously created on the switch.
<view_name 32> − An alphanumeric string of up to 32 characters
that identifies the SNMP view to be deleted.
all − Specifies that all of the SNMP views on the switch will be
deleted.
<oid> − The object ID that identifies an object tree (MIB tree) that
will be deleted from the switch.
DES-3550:4#delete snmp view dlinkview all
Command: delete snmp view dlinkview all
Success.
DES-3550:4#
command is used to remove an SNMP view
Example usage:
To display SNMP view configuration:
show snmp view
Purpose Used to display an SNMP view previously created on the switch.
Syntax
Description
Parameters
Restrictions None.
DES-3550:4#show snmp view
Command: show snmp view
Vacm View Table Settings
View Name Subtree View Type
-------------------- ------------------------- --------- ReadView 1 Included
WriteView 1 Included
NotifyView 1.3.6 Included
restricted 1.3.6.1.2.1.1 Included
restricted 1.3.6.1.2.1.11 Included
show snmp view {<view_name 32>}
The
show snmp view
created on the switch in the VACM View Table Settings.
<view_name 32> − An alphanumeric string of up to 32 characters
that identifies the SNMP view that will be displayed.
command displays an SNMP view previously
32
Page 41
restricted 1.3.6.1.6.3.10.2.1 Included
restricted 1.3.6.1.6.3.11.2.1 Included
restricted 1.3.6.1.6.3.15.1.1 Included
CommunityView 1 Included
CommunityView 1.3.6.1.6.3 Excluded
CommunityView 1.3.6.1.6.3.1 Included
Total Entries: 11
DES-3550:4#
create snmp community
Purpose Used to create an SNMP community string to define the relationship
between the SNMP manager and an agent. The community string
acts like a password to permit access to the agent on the switch.
One or more of the following characteristics can be associated with
the community string:
An Access List of IP addresses of SNMP managers that are
permitted to use the community string to gain access to the switch’s
SNMP agent.
An MIB view that defines the subset of all MIB objects that will be
accessible to the SNMP community.
Syntax
Description
Parameters
Read|write or read-only level permission for the MIB objects
accessible to the SNMP community.
create snmp community <community_string 32> view
<view_name 32> [read_only | read_write]
The
create snmp community
community string and to assign access-limiting characteristics to this
community string.
<community_string 32> − An alphanumeric string of up to 32
characters that is used to identify members of an SNMP community.
This string is used like a password to give remote SNMP managers
access to MIB objects in the switch’s SNMP agent.
<view_name 32> − An alphanumeric string of up to 32 characters
that is used to identify the group of MIB objects that a remote SNMP
manager is allowed to access on the switch.
read_only − Specifies that SNMP community members using the
community string created with this command can only read the
contents of the MIBs on the switch.
read_write − Specifies that SNMP community members using the
community string created with this command can read from and
write to the contents of the MIBs on the switch.
command is used to create an SNMP
Restrictions Only administrator-level users can issue this command.
Example usage:
To create the SNMP community string “dlink:”
33
Page 42
DES-3550:4#create snmp community dlink view ReadView
read_write
Command: create snmp community dlink view ReadView
read_write
Success.
delete snmp community
Purpose Used to remove a specific SNMP community string from the switch.
Example usage:
To delete the SNMP community string “dlink:”
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
delete snmp community <community_string 32>
The
delete snmp community
previously defined SNMP community string from the switch.
<community_string 32> − An alphanumeric string of up to 32
characters that is used to identify members of an SNMP community.
This string is used like a password to give remote SNMP managers
access to MIB objects in the switch’s SNMP agent.
DES-3550:4#delete snmp community dlink
Command: delete snmp community dlink
Success.
DES-3550:4#
command is used to remove a
show snmp community
Purpose Used to display SNMP community strings configured on the switch.
Syntax
Description
Parameters
Restrictions None.
Example usage:
To display the currently entered SNMP community strings:
show snmp community {<community_string 32>}
The
community strings that are configured on the switch.
<community_string 32> − An alphanumeric string of up to 32
characters that is used to identify members of an SNMP community.
This string is used like a password to give remote SNMP managers
access to MIB objects in the switch’s SNMP agent.
show snmp community
34
command is used to display SNMP
Page 43
DES-3550:4#show snmp community
Command: show snmp community
SNMP Community Table
Community Name View Name Access Right
-------------------------------- -------------------------------- ------------
dlink ReadView read_write
private CommunityView read_write
public CommunityView read_only
Total Entries: 3
DES-3550:4#
config snmp engineID
Purpose Used to configure a name for the SNMP engine on the switch.
Example usage:
To give the SNMP agent on the switch the name “0035636666”
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
config snmp engineID <snmp_engineID>
The
config snmp engineID
SNMP engine on the switch.
<snmp_engineID> − An alphanumeric string that will be used to
identify the SNMP engine on the switch.
DES-3550:4#config snmp 0035636666
Command: config snmp engineID 0035636666
Success.
DES-3550:4#
command configures a name for the
show snmp engineID
Purpose Used to display the identification of the SNMP engine on the switch.
Syntax
Description
Parameters None.
show snmp engineID
The
show snmp engineID
the SNMP engine on the switch.
command displays the identification of
35
Page 44
Example usage:
To display the current name of the SNMP engine on the switch:
create snmp group
Purpose Used to create a new SNMP group, or a table that maps SNMP users
show snmp engineID
Restrictions None.
DES-3550:4#show snmp engineID
Command: show snmp engineID
SNMP Engine ID : 0035636666
DES-3550:4#
to SNMP views. This will set then entry in the VACM Access Table
Settings.
Syntax
Description
Parameters
create snmp group <groupname 32> [v1|v2c|v3 [noauth_nopriv |
auth_nopriv | auth_priv]] {read_view <view_name 32> |
write_view <view_name 32> | notify_view <view_name 32>}
The
create snmp group
table that maps SNMP users to SNMP views.
<groupname 32> − An alphanumeric name of up to 32 characters
that will identify the SNMP group the new SNMP user will be
associated with.
v1 – Specifies that SNMP version 1 will be used. The Simple
Network Management Protocol (SNMP), version 1, is a network
management protocol that provides a means to monitor and control
network devices.
v2c – Specifies that SNMP version 2c will be used. The SNMP v2c
supports both centralized and distributed network management
strategies. It includes improvements in the Structure of Management
Information (SMI) and adds some security features.
v3 – Specifies that the SNMP version 3 will be used. SNMP v3
provides secure access to devices through a combination of
authentication and encrypting packets over the network. SNMP v3
adds:
Message integrity − ensures that packets have not been tampered
with during transit.
command creates a new SNMP group, or a
Authentication − determines if an SNMP message is from a valid
source.
Encryption − scrambles the contents of messages to prevent it being
viewed by an unauthorized source.
noauth_nopriv − Specifies that there will be no authorization and no
encryption of packets sent between the switch and a remote SNMP
36
Page 45
create snmp group
manager.
auth_nopriv − Specifies that authorization will be required, but there
will be no encryption of packets sent between the switch and a
remote SNMP manager.
auth_priv − Specifies that authorization will be required, and that
packets sent between the switch and a remote SNMP manger will be
encrypted.
read_view – Specifies that the SNMP group being created can
request SNMP messages.
write_view – Specifies that the SNMP group being created has write
privileges.
<view_name 32> − An alphanumeric string of up to 32 characters that
is used to identify the group of MIB objects that a remote SNMP
manager is allowed to access on the switch.
notify_view − Specifies that the SNMP group being created can
receive SNMP trap messages generated by the switch’s SNMP
agent.
Restrictions Only administrator-level users can issue this command.
Example usage:
To create an SNMP group named “sg1:”
DES-3550:4#create snmp group sg1 v3 noauth_nopriv read_view v1
write_view v1 notify_view v1
Command: create snmp group sg1 v3 noauth_nopriv read_view v1
write_view v1 notify_view v1
Success.
DES-3550:4#
delete snmp group
Purpose Used to remove an SNMP group from the switch.
Syntax
Description
delete snmp group <groupname 32>
The
delete snmp group
group from the switch.
command is used to remove an SNMP
Parameters
Restrictions Only administrator-level users can issue this command.
Example usage:
<groupname 32> − An alphanumeric name of up to 32 characters
that will identify the SNMP group the new SNMP user will be
associated with.
37
Page 46
To delete the SNMP group named “sg1”.
DES-3550:4#delete snmp group sg1
Command: delete snmp group sg1
Success.
DES-3550:4#
show snmp groups
Purpose Used to display the group-names of SNMP groups currently
configured on the switch. The security model, level, and status of
each group are also displayed.
Example usage:
To display the currently configured SNMP groups on the switch:
Syntax
Description
Parameters None.
Restrictions None.
DES-3550:4#show snmp groups
Command: show snmp groups
Vacm Access Table Settings
Group Name : Group3
ReadView Name : ReadView
WriteView Name : WriteView
Notify View Name : NotifyView
Security Model : SNMPv3
Security Level : NoAuthNoPriv
Group Name : Group4
ReadView Name : ReadView
WriteView Name : WriteView
Notify View Name : NotifyView
Security Model : SNMPv3
Security Level : authNoPriv
Group Name : Group5
ReadView Name : ReadView
WriteView Name : WriteView
Notify View Name : NotifyView
Security Model : SNMPv3
Security Level : authNoPriv
Group Name : Group6
ReadView Name : ReadView
show snmp groups
The
show snmp groups
SNMP groups currently configured on the switch. The security
model, level, and status of each group are also displayed.
command displays the group-names of
38
Page 47
WriteView Name : WriteView
Notify View Name : NotifyView
Security Model : SNMPv3
Security Level : authPriv
Group Name : Group7
ReadView Name : ReadView
WriteView Name : WriteView
Notify View Name : NotifyView
Security Model : SNMPv3
Security Level : authPriv
Group Name : initial
ReadView Name : restricted
WriteView Name :
Notify View Name : restricted
Security Model : SNMPv3
Security Level : NoAuthNoPriv
Group Name : ReadGroup
ReadView Name : CommunityView
WriteView Name :
Notify View Name : CommunityView
Security Model : SNMPv1
Security Level : NoAuthNoPriv
Group Name : ReadGroup
ReadView Name : CommunityView
WriteView Name :
Notify View Name : CommunityView
Security Model : SNMPv2
Security Level : NoAuthNoPriv
Group Name : WriteGroup
ReadView Name : CommunityView
WriteView Name : CommunityView
Notify View Name : CommunityView
Security Model : SNMPv1
Security Level : NoAuthNoPriv
Group Name : WriteGroup
ReadView Name : CommunityView
WriteView Name : CommunityView
Notify View Name : CommunityView
Security Model : SNMPv2
Security Level : NoAuthNoPriv
Total Entries: 10
DES-3550:4#
create snmp host
Purpose Used to create a recipient of SNMP traps generated by the switch’s
Syntax
SNMP agent.
create snmp host <ipaddr> [v1 | v2c | v3 [noauth_nopriv |
39
Page 48
create snmp host
auth_nopriv | auth_priv] <auth_string 32>]
Description
Parameters
The
create snmp host
generated by the switch’s SNMP agent.
<ipaddr> − The IP address of the remote management station that
will serve as the SNMP host for the switch.
v1 – Specifies that SNMP version 1 will be used. The Simple
Network Management Protocol (SNMP), version 1, is a network
management protocol that provides a means to monitor and control
network devices.
v2c – Specifies that SNMP version 2c will be used. The SNMP v2c
supports both centralized and distributed network management
strategies. It includes improvements in the Structure of
Management Information (SMI) and adds some security features.
v3 – Specifies that the SNMP version 3 will be used. SNMP v3
provides secure access to devices through a combination of
authentication and encrypting packets over the network. SNMP v3
adds:
Message integrity − ensures that packets have not been tampered
with during transit.
Authentication − determines if an SNMP message is from a valid
source.
command creates a recipient of SNMP traps
Example usage:
To create an SNMP host to receive SNMP messages:
Encryption − scrambles the contents of messages to prevent it being
viewed by an unauthorized source.
noauth_nopriv − Specifies that there will be no authorization and no
encryption of packets sent between the switch and a remote SNMP
manager.
auth_nopriv − Specifies that authorization will be required, but there
will be no encryption of packets sent between the switch and a
remote SNMP manager.
auth_priv − Specifies that authorization will be required, and that
packets sent between the switch and a remote SNMP manger will
be encrypted.
<auth_sting 32> − An alphanumeric string used to authorize a
remote SNMP manager to access the switch’s SNMP agent.
Restrictions Only administrator-level users can issue this command.
40
Page 49
DES-3550:4#create snmp host 10.48.74.100 v3 auth_priv public
Command: create snmp host 10.48.74.100 v3 auth_priv public
Success.
DES-3550:4#
delete snmp host
Purpose Used to remove a recipient of SNMP traps generated by the switch’s
SNMP agent.
Example usage:
To delete an SNMP host entry:
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
DES-3550:4#delete snmp host 10.48.74.100
Command: delete snmp host 10.48.74.100
Success.
DES-3550:4#
delete snmp host <ipaddr>
The
delete snmp host
generated by the switch’s SNMP agent.
<ipaddr> − The IP address of a remote SNMP manager that will
receive SNMP traps generated by the switch’s SNMP agent.
command deletes a recipient of SNMP traps
show snmp host
Purpose Used to display the recipient of SNMP traps generated by the
switch’s SNMP agent.
Syntax
Description
Parameters
Restrictions None.
Example usage:
To display the currently configured SNMP hosts on the switch:
show snmp host {<ipaddr>}
The
show snmp host
and configuration information of remote SNMP managers that are
designated as recipients of SNMP traps that are generated by the
switch’s SNMP agent.
<ipaddr> − The IP address of a remote SNMP manager that will
receive SNMP traps generated by the switch’s SNMP agent.
command is used to display the IP addresses
41
Page 50
DES-3550:4#show snmp host
Command: show snmp host
SNMP Host Table
Host IP Address SNMP Version Community Name/SNMPv3
User Name
--------------- --------------------- ------------------------------
10.48.76.23 V2c private
10.48.74.100 V3 authpriv public
Total Entries: 2
DES-3550:4#
create trusted_host
Purpose Used to create the trusted host.
Example usage:
To create the trusted host:
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
DES-3550:4#create trusted_host 10.48.74.121
Command: create trusted_host 10.48.74.121
Success.
DES-3550:4#
create trusted_host <ipaddr>
The
create trusted_host
switch allows you to specify up to four IP addresses that are allowed
to manage the switch via in-band SNMP or TELNET based
management software. These IP addresses must be members of
the Management VLAN. If no IP addresses are specified, then there
is nothing to prevent any IP address from accessing the switch,
provided the user knows the Username and Password.
<ipaddr> − The IP address of the trusted host.
command creates the trusted host. The
show trusted_host
Purpose Used to display a list of trusted hosts entered on the switch using the
create trusted_host
Syntax
Description This command is used to display a list of trusted hosts entered on
show trusted_host <ipaddr>
command above.
42
Page 51
show trusted_host
the switch using the
create trusted_host
command above.
Parameters
Restrictions none.
Example Usage:
To display the list of trust hosts:
delete trusted_host
<ipaddr> − The IP address of the trusted host.
DES-3550:4#show trusted_host
Command: show trusted_host
Management Stations
IP Address
-----------------------
10.53.13.94
Total Entries: 1
DES-3550:4#
Purpose Used to delete a trusted host entry made using the create
Syntax
Description This command is used to delete a trusted host entry made using the
Parameters
Restrictions Only administrator-level users can issue this command.
Example Usage:
To delete a trusted host with an IP address 10.48.74.121:
enable snmp traps
trusted_host command above.
delete trusted _host <ipaddr>
create trusted_host command above.
<ipaddr> − The IP address of the trusted host.
DES-3550:4#delete trusted_host 10.48.74.121
Command: delete trusted_host 10.48.74.121
Success.
DES-3550:4#
Purpose Used to enable SNMP trap support.
43
Page 52
enable snmp traps
Syntax
Description The enable snmp traps command is used to enable SNMP trap
Parameters none.
Restrictions Only administrator-level users can issue this command.
Example usage:
To enable SNMP trap support on the switch:
DES-3550:4#enable snmp traps
Command: enable snmp traps
Success.
DES-3550:4#
enable snmp traps
support on the switch.
enable snmp authenticate_traps
Purpose Used to enable SNMP authentication trap support.
Syntax
Description This command is used to enable SNMP authentication trap support
Parameters none.
Restrictions Only administrator-level users can issue this command.
Example Usage:
To turn on SNMP authentication trap support:
show snmp traps
Purpose Used to show SNMP trap support on the switch .
enable snmp authenticate_traps
on the Switch.
DES-3550:4#enable snmp authenticate_traps
Command: enable snmp authenticate_traps
Success.
DES-3550:4#
Syntax
Description This command is used to view the SNMP trap support status
show snmp traps
44
Page 53
show snmp traps
currently configured on the Switch.
Parameters none.
Restrictions Only administrator-level users can issue this command.
Example usage:
To view the current SNMP trap support:
DES-3550:4#show snmp traps
Command: show snmp traps
SNMP Traps : Enabled
Authenticate Traps : Enabled
DES-3550:4#
disable snmp traps
Example Usage:
To prevent SNMP traps from being sent from the Switch:
disable snmp authenticate_traps
Purpose Used to disable SNMP trap support on the switch.
Syntax
Description This command is used to disable SNMP trap support on the Switch.
Parameters none.
Restrictions Only administrator-level users can issue this command.
DES-3550:4#disable snmp traps
Command: disable snmp traps
Success.
DES-3550:4#
disable snmp traps
Purpose Used to disable SNMP authentication trap support.
Syntax
Description This command is used to disable SNMP authentication support on
disable snmp authenticate_traps
the Switch.
45
Page 54
disable snmp authenticate_traps
Parameters none.
Restrictions Only administrator-level users can issue this command.
Example Usage:
To disable the SNMP authentication trap support:
config snmp system_contact
Purpose Used to enter the name of a contact person who is responsible for
DES-3550:4#disable snmp authenticate_traps
Command: disable snmp authenticate_traps
Success.
DES-3550:4#
the switch.
Syntax
Description The config snmp system_contact command is used to enter the
Parameters <sw_contact> - A maximum of 255 characters is allowed. A NULL
Restrictions Only administrator-level users can issue this command.
Example usage:
To configure the switch contact to “
DES-3550:4#config snmp system_contact MIS Department II
Command: config snmp system_contact MIS Department II
Success.
DES-3550:4#
config snmp system_contact{<sw_contact>}
name and/or other information to identify a contact person who is
responsible for the switch. A maximum of 255 character can be
used.
string is accepted if there is no contact.
MIS Department II
”:
config snmp system_location
Purpose Used to enter a description of the location of the switch.
Syntax
Description The config snmp system_location command is used to enter a
config snmp system_location {<sw_location>}
description of the location of the switch. A maximum of 255
46
Page 55
config snmp system_location
Parameters <sw_location> - A maximum of 255 characters is allowed. A NULL
Restrictions Only administrator-level users can issue this command.
Example usage:
characters can be used.
string is accepted if there is no location desired.
To configure the switch location for “
DES-3550:4#config snmp system_location HQ 5F
Command: config snmp system_location HQ 5F
Success.
DES-3550:4#
HQ 5F
”:
config snmp system_name
Purpose Used to configure the name for the switch.
Syntax
Description The config snmp system_name command configures the name of
Parameters <sw_name> - A maximum of 255 characters is allowed. A NULL
Restrictions Only administrator-level users can issue this command.
config snmp system_name {<sw_name>}
the switch.
string is accepted if no name is desired.
Example usage:
To configure the switch name for “
DES-3550:4#config snmp system_name DES-3550 Switch
Command: config snmp system_name DES-3550 Switch
Success.
DES-3550:4#
enable rmon
Purpose Used to enable RMON on the switch.
Syntax
enable rmon
DES-3550 Switch
47
”:
Page 56
enable rmon
Description This command is used, in conjunction with the disable rmon
Parameters none.
Restrictions Only administrator-level users can issue this command.
Example Usage:
command below, to enable and disable remote monitoring (RMON)
on the switch.
To enable RMON:
disable rmon
Purpose Used to disable RMON on the switch.
Syntax
Description This command is used, in conjunction with the enable rmon
Parameters none.
Restrictions Only administrator-level users can issue this command.
DES-3550:4#enable rmon
Command: enable rmon
Success.
DES-3550:4#
disable rmon
command above, to enable and disable remote monitoring (RMON)
on the switch.
Example Usage:
To disable RMON:
DES-3550:4#disable rmon
Command: disable rmon
Success.
DES-3550:4#
48
Page 57
8
SWITCH UTILITY COMMANDS
The download/upload commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in the
following table.
Command Parameters
download [ firmware <ipaddr> <path_filename 64> {section_id <int 1-2>}
configuration <ipaddr> <path_filename 64> {increment} ]
config firmware section_id <value 1-2> [delete | boot_up]
show
firmware_information
upload [ configuration | log ] <ipaddr> <path_filename 64>
ping <ipaddr> {times <value 1-255>} {timeout <sec 1-99>}
Each command is listed, in detail, in the following sections.
download
Purpose Used to download and install new firmware or a switch configuration
file from a TFTP server.
Syntax
Description This command is used to download a new firmware or a switch
Parameters
download[ firmware <ipaddr> <path_filename 64> {section_id
<int 1-2>} configuration <ipaddr> <path_filename 64>
{increment} ]
configuration file from a TFTP server.
firmware − Download and install new firmware on the switch from a
TFTP server.
configuration − Download a switch configuration file from a TFTP
server.
<ipaddr> − The IP address of the TFTP server.
Restrictions The TFTP server must be on the same IP subnet as the switch. Only
Example usage:
<path_filename> − The DOS path and filename of the firmware or
switch configuration file on the TFTP server. For example,
C:\3550.had.
section_id <int 1-2> - Specify the working section id. The Switch can
hold two firmware versions for the user to select from, which are
specified by section id.
increment − Allows the download of a partial switch configuration file.
This allows a file to be downloaded that will change only the switch
parameters explicitly stated in the configuration file. All other switch
parameters will remain unchanged.
administrator-level users can issue this command.
49
Page 58
To download a configuration file:
DES-3550:4#download configuration 10.48.74.121 c:\cfg\setting.txt
Command: download configuration 10.48.74.121 c:\cfg\setting.txt
Connecting to server................... Done.
Download configuration............. Done.
DES-3550:4#
config firmware
Purpose Used to configure the firmware section as a boot up section, or to
delete the firmware section
Syntax
Description This command is used to configure the firmware section. The user
Parameters section_id – Specifies the working section. The Switch can hold two
Restrictions Only administrator-level users can issue this command.
Example usage:
To configure firmware section 1 as a boot up section:
DES-3550:4# config firmware section_id 1 boot_up
Command: config firmware section_id 1 boot_up
Success.
DES-3550:4#
config firmware section_id <int 1-2> [delete | boot_up]
may choose to remove the firmware section or use it as a boot up
section.
firmware versions for the user to select from, which are specified by
section id.
delete – Entering this parameter will delete the specified firmware
section.
boot_up – Entering this parameter will specify the firmware section id
as a boot up section.
show firmware information
Purpose Used to display the firmware section information.
Syntax
Description This command is used to display the firmware section information
Parameters None.
show firmware information
50
Page 59
show firmware information
Restrictions None.
Example usage:
To display the current firmware information on the switch:
DES-3550:4#show firmware information
Command: show firmware information
ID Version Size(B) Update Time From User
-- -------- ------- ------------------- ------------------ ---------------
1 1.00-B00 1360471 00000 days 00:00:00 Serial Port (PROM) Unknown
*2 1.00-B02 2052372 00000 days 00:00:56 10.53.13.94
Anonymous
'*' means boot up section
(T) means firmware update thru TELNET
(S) means firmware update thru SNMP
(W) means firmware update thru WEB
Free space: 3145728 bytes
DES-3550:4#
Example usage:
upload
Purpose Used to upload the current switch settings or the switch history log to
a TFTP.
Syntax
Description This command is used to upload either the switch’s current settings
Parameters
Restrictions The TFTP server must be on the same IP subnet as the switch.
upload [ configuration | log ] <ipaddr> <path_filename 64>
or the switch’s history log to a TFTP server.
configuration − Specifies that the switch’s current settings will be
uploaded to the TFTP server.
log − Specifies that the switch history log will be uploaded to the
TFTP server.
<ipaddr> − The IP address of the TFTP server. The TFTP server
must be on the same IP subnet as the switch.
<path_filename> − Specifies the location of the switch configuration
file on the TFTP server. This file will be replaced by the uploaded file
from the switch.
Only administrator-level users can issue this command.
51
Page 60
To upload a configuration file:
DES-3550:4#upload configuration 10.48.74.121 c:\cfg\log.txt
Command: upload configuration 10.48.74.121 c:\cfg\log.txt
Connecting to server................... Done.
Upload configuration...................Done.
DES-3550:4#
ping
Purpose Used to test the connectivity between network devices.
Example usage:
To ping a device with the IP address 10.48.74.121 four times:
Syntax
Description The ping command sends Internet Control Message Protocol (ICMP)
Parameters <ipaddr> - Specifies the IP address of the host.
Restrictions None.
DES-3550:4#ping 10.48.74.121 times 4
Command: ping 10.48.74.121
Reply from 10.48.74.121, time<10ms
Reply from 10.48.74.121, time<10ms
Reply from 10.48.74.121, time<10ms
Reply from 10.48.74.121, time<10ms
Ping statistics for 10.48.74.121
Packets: Sent =4, Received =4, Lost =0
DES-3550:4#
ping <ipaddr> {times <value 1-255>} {timeout <sec 1-99>}
echo messages to a remote IP address. The remote IP address will
then “echo” or return the message. This is used to confirm
connectivity between the switch and the remote device.
times - The number of individual ICMP echo messages to be sent.
A value of 0 will send an infinite ICMP echo messages. The
maximum value is 255. The default is 0.
timeout - Defines the time-out period while waiting for a response
from the remote device.
A value of 1 to 99 seconds can be specified. The default is 1 second
52
Page 61
9
NETWORK MONITORING COMMANDS
The network monitoring commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in
the following table.
Command Parameters
show packet ports <portlist>
show error ports <portlist>
show utilitzation [cpu | ports {<portlist>}]
clear counters ports <portlist>
clear log
show log index <value_list>
enable syslog
disable syslog
show syslog
create syslog host <index 1-4> ipaddress <ipaddr> {severity
[informational|warning|all]| facility[local0|local1|local2|local3|
local4|local5|local6|local7] |udp_port<udp_port_number>|
state[enable|disable]
config syslog host
delete syslog host
show syslog host
Each command is listed, in detail, in the following sections.
[all | <index 1-4>] {severity [informational | warning |all] |facility
[local0|local1|local2|local3|local4|local5|local6|local7] |udp_port
<udp_port_number> | ipaddress <ipaddr> | state [enable |
disable]}
<index 1-4>
all
<index 1-4>
show packet ports
Purpose Used to display statistics about the packets sent
and received by the switch.
Syntax
Description This command is used to display statistics about
Parameters
show packet ports <portlist>
packets sent and received by ports specified in
the port list.
<portlist> − specifies a port or range of ports to
be displayed.
Restrictions None.
Example usage:
To display the packets analysis for port 7 of module 2:
53
Page 62
DES-3550:4#show packet port 2
Port number : 2
Frame Size Frame Counts Frame/sec Frame Type Total Total/sec
------------ ------------ ---------- ---------- ------- ---------
64 3275 10 RX Bytes 408973 1657
65-127 755 10 RX Frames 395 19
128-255 316 1
256-511 145 0 TX Bytes 7918 178
512-1023 15 0 TX Frames 111 2
1024-1518 0 0
Unicast RX 152 1
Multicast RX 557 2
Broadcast RX 3686 16
DES-3550:4#
show error ports
Example usage:
To display the errors of port 3:
Purpose Used to display the error statistics for a range of ports.
Syntax
Description This command will display all of the packet error statistics collected
Parameters
Restrictions None.
DES-3550:4#show errors port 3
RX Frames TX Frames
--------------- ----------------
CRC Error 19 Excessive Deferral 0
Undersize 0 CRC Error 0
Oversize 0 Late Collision 0
Fragment 0 Excessive Collision 0
Jabber 11 Single Collision 0
Drop Pkts 20837 Collision 0
DES-3550:4#
show error ports <portlist>
and logged by the switch for a given port list.
<portlist> − specifies a port or range of ports to be displayed.
54
Page 63
show utilization
Purpose Used to display real-time port and cpu utilization statistics.
Example usage:
To display the port utilization statistics:
Syntax
Description This command will display the real-time port and cpu utilization
Parameters cpu – Entering this parameter will display the current cpu utilization
Restrictions None.
DES-3550:4#show utilization ports
Command: show utilization ports
Port TX/sec RX/sec Util Port TX/sec RX/sec Util
------ ---------- ---------- ---- ------ ---------- ---------- ----
1 0 0 0 22 0 0 0
2 0 0 0 23 0 0 0
3 0 0 0 24 0 0 0
4 0 0 0 25 0 26 1
5 0 0 0 26 0 0 0
6 0 0 0 27 0 0 0
7 0 0 0 28 0 0 0
8 0 0 0 29 0 0 0
9 0 0 0 30 0 0 0
10 0 0 0 31 0 0 0
11 0 0 0 32 0 0 0
12 0 0 0 33 0 0 0
13 0 0 0 34 0 0 0
14 0 0 0 35 0 0 0
15 0 0 0 36 0 0 0
16 0 0 0 37 0 0 0
17 0 0 0 38 0 0 0
18 0 0 0 39 0 0 0
19 0 0 0 40 0 0 0
20 0 0 0 41 0 0 0
21 0 0 0 42 0 0 0
CTRL+C ESC q Quit Space n Next Page p Previous Page r Refresh
show utilization [cpu | ports {<portlist>}]
statistics for the switch.
of the switch.
ports - Entering this parameter will display the current port
utilization of the switch.
<portlist> Specifies a port or range of ports to be displayed.
55
Page 64
To display the current cpu utilization:
DES-3550:4#show utilization cpu
Command: show utilization cpu
CPU utilization :
-------------------------------------------------------------------------------
Five seconds - 15% One minute - 25% Five minutes - 14%
DES-3550:4#
clear counters
Purpose Used to clear the switch’s statistics counters.
Example usage:
To clear the counters:
Syntax
Description This command will clear the counters used by the switch to compile
Parameters
Restrictions Only administrator-level users can issue this command.
DES-3550:4#clear counters ports 2-9
Command: clear counters ports 2-9
Success.
DES-3550:4#
clear counters {ports <portlist>}
statistics.
<portlist> − specifies a port or range of ports to be displayed.
clear log
Purpose Used to clear the switch’s history log.
Syntax
clear log
Description This command will clear the switch’s history log.
Parameters None.
Restrictions Only administrator-level users can issue this command.
Example usage:
To clear the log information:
56
Page 65
DES-3550:4#clear log
Command: clear log
Success.
DES-3550:4#
show log
Purpose Used to display the switch history log.
Syntax
Description This command will display the contents of the switch’s history log.
Parameters
Restrictions None.
Example usage:
To display the switch history log:
DES-3550:4#show log index 5
Command: show log index 5
Index Time Log Text
----- ------------------- ----------------------------------------------------
5 00000 days 00:01:09 Successful login through Console (Username: Anonymous)
4 00000 days 00:00:14 System started up
3 00000 days 00:00:06 Port 1 link up, 100Mbps FULL duplex
2 00000 days 00:00:01 Spanning Tree Protocol is disabled
1 00000 days 00:06:31 Configuration saved to flash (Username: Anonymous)
DES-3550:4#
show log {index <value>}
index <value> − This command will display the history log, beginning
at 1 and ending at the value specified by the user in the <value> field.
If no parameter is specified, all history log entries will be displayed.
enable syslog
Purpose Used to enable the system log to be sent to a remote host.
Syntax
Description
Parameters None.
Restrictions Only administrator-level users can issue this command.
enable syslog
The
enable syslog
remote host.
command enables the system log to be sent to a
57
Page 66
Example usage:
To the syslog function on the switch:
DES-3550:4#enable syslog
Command: enable syslog
Success.
DES-3550:4#
disable syslog
Purpose Used to enable the system log to be sent to a remote host.
Example usage:
To disable the syslog function on the switch:
Syntax
Description
Parameters None.
Restrictions Only administrator-level users can issue this command.
disable syslog
The
disable syslog
a remote host.
DES-3550:4#disable syslog
Command: disable syslog
Success.
DES-3550:4#
command enables the system log to be sent to
show syslog
Purpose Used to display the syslog protocol status as enabled or disabled.
Syntax
Description
Parameters None.
Restrictions None.
Example usage:
To display the current status of the syslog function:
show syslog
The
or disabled.
show syslog
command displays the syslog status as enabled
58
Page 67
DES-3550:4#show syslog
Command: show syslog
Syslog Global State: Enabled
DES-3550:4#
create syslog host
Purpose Used to create a new syslog host.
Syntax
Description
Parameters
create syslog host <index 1-4> ipaddress <ipaddr> {severity
[informational|warning|all]| facility[local0|local1|local2|local3|
local4|local5|local6|local7] |udp_port<udp_port_number>|
state[enable|disable]
The
create syslog host
host.
<index 1-4> − Specifies that the command will be applied to an index
of hosts. There are four available indexes, numbered 1 through 4.
ipaddress <ipaddr> − Specifies the IP address of the remote host
where syslog messages will be sent.
severity − Severity level indicator. These are described in the
following:
Bold font indicates that the corresponding severity level is currently
supported on the switch.
Numerical Severity
Code
0 Emergency: system is unusable
1 Alert: action must be taken immediately
2 Critical: critical conditions
command is used to create a new syslog
3 Error: error conditions
4 Warning: warning conditions
5 Notice: normal but significant condition
6 Informational: informational messages
7 Debug: debug-level messages
informational − Specifies that informational messages will be sent to
the remote host. This corresponds to number 6 from the list above.
warning − Specifies that warning messages will be sent to the
remote host. This corresponds to number 4 from the list above.
all − Specifies that all of the currently supported syslog messages
that are generated by the switch will be sent to the remote host.
59
Page 68
create syslog host
facility − Some of the operating system daemons and processes
have been assigned Facility values. Processes and daemons that
have not been explicitly assigned a Facility may use any of the"local
use" facilities or they may use the "user-level" Facility. Those
Facilities that have been designated are shown in the following: Bold
font indicates the facility values that the switch currently supports.
Numerical Facility
Code
0 kernel messages
1 user-level messages
2 mail system
3 system daemons
4 security|authorization messages
5 messages generated internally by syslog
6 line printer subsystem
7 network news subsystem
8 UUCP subsystem
9 clock daemon
10 security|authorization messages
11 FTP daemon
12 NTP subsystem
13 log audit
14 log alert
15 clock daemon
16 local use 0 (local0)
17 local use 1 (local1)
18 local use 2 (local2)
19 local use 3 (local3)
20 local use 4 (local4)
21 local use 5 (local5)
22 local use 6 (local6)
23 local use 7 (local7)
local0 − Specifies that local use 0 messages will be sent to the
60
Page 69
create syslog host
remote host. This corresponds to number 16 from the list above.
local1 − Specifies that local use 1 messages will be sent to the
remote host. This corresponds to number 17 from the list above.
local2 − Specifies that local use 2 messages will be sent to the
remote host. This corresponds to number 18 from the list above.
local3 − Specifies that local use 3 messages will be sent to the
remote host. This corresponds to number 19 from the list above.
local4 − Specifies that local use 4 messages will be sent to the
remote host. This corresponds to number 20 from the list above.
local5 − Specifies that local use 5 messages will be sent to the
remote host. This corresponds to number 21 from the list above.
local6 − Specifies that local use 6 messages will be sent to the
remote host. This corresponds to number 22 from the list above.
local7 − Specifies that local use 7 messages will be sent to the
remote host. This corresponds to number 23 from the list above.
Example usage:
To create syslog host:
udp_port <udp_port_number> − Specifies the UDP port number that
the syslog protocol will use to send messages to the remote host.
state [enable | disable] − Allows the sending of syslog messages to
the remote host, specified above, to be enabled and disabled.
Restrictions Only administrator-level users can issue this command.
DES-3550:4#create syslog host 1 severity all facility local0
Command: create syslog host 1 severity all facility local0
Success.
DES-3550:4#
config syslog host
Purpose
Used to configure the syslog protocol to send system log data to a
remote host.
Syntax
Description
Parameters
config syslog host [all | <index 1-4>] {severity [informational |
warning | all] | facility [local0|local1|local2|local3|
local4|local5|local6|local7] | udp_port<udp_port_number> |
ipaddress <ipaddr> | state [enable | disable]
The
config syslog host
protocol to send system log information to a remote host.
all − Specifies that the command will be applied to all hosts.
command is used to configure the syslog
61
Page 70
config syslog host
<index 1-4> − Specifies that the command will be applied to an index
of hosts. There are four available indexes, numbered 1 through 4.
severity − Severity level indicator. These are described in the
following:
Bold font indicates that the corresponding severity level is currently
supported on the switch.
Numerical Severity
Code
0 Emergency: system is unusable
1 Alert: action must be taken immediately
2 Critical: critical conditions
3 Error: error conditions
4 Warning: warning conditions
5 Notice: normal but significant condition
6 Informational: informational messages
7 Debug: debug-level messages
informational − Specifies that informational messages will be sent to
the remote host. This corresponds to number 6 from the list above.
warning − Specifies that warning messages will be sent to the
remote host. This corresponds to number 4 from the list above.
all − Specifies that all of the currently supported syslog messages
that are generated by the switch will be sent to the remote host.
facility − Some of the operating system daemons and processes
have been assigned Facility values. Processes and daemons that
have not been explicitly assigned a Facility may use any of the"local
use" facilities or they may use the "user-level" Facility. Those
Facilities that have been designated are shown in the following: Bold
font indicates that the facility values the switch currently supports.
Numerical Facility
Code
0 kernel messages
1 user-level messages
2 mail system
3 system daemons
4 security|authorization messages
5 messages generated internally by syslog
6 line printer subsystem
7 network news subsystem
8 UUCP subsystem
9 clock daemon
10 security|authorization messages
62
Page 71
config syslog host
11 FTP daemon
12 NTP subsystem
13 log audit
14 log alert
15 clock daemon
16 local use 0 (local0)
17 local use 1 (local1)
18 local use 2 (local2)
19 local use 3 (local3)
20 local use 4 (local4)
21 local use 5 (local5)
22 local use 6 (local6)
23 local use 7 (local7)
local0 − Specifies that local use 0 messages will be sent to the
remote host. This corresponds to number 16 from the list above.
local1 − Specifies that local use 1 messages will be sent to the
remote host. This corresponds to number 17 from the list above.
Example usage:
Restrictions
local2 − Specifies that local use 2 messages will be sent to the
remote host. This corresponds to number 18 from the list above.
local3 − Specifies that local use 3 messages will be sent to the
remote host. This corresponds to number 19 from the list above.
local4 − Specifies that local use 4 messages will be sent to the
remote host. This corresponds to number 20 from the list above.
local5 − Specifies that local use 5 messages will be sent to the
remote host. This corresponds to number 21 from the list above.
local6 − Specifies that local use 6 messages will be sent to the
remote host. This corresponds to number 22 from the list above.
local7 − Specifies that local use 7 messages will be sent to the
remote host. This corresponds to number 23 from the list above.
udp_port <udp_port_number> − Specifies the UDP port number that
the syslog protocol will use to send messages to the remote host.
ipaddress <ipaddr> − Specifies the IP address of the remote host
where syslog messages will be sent.
state [enable | disable] − Allows the sending of syslog messages to
the remote host, specified above, to be enabled and disabled.
Only administrator-level users can issue this command.
To configure a syslog host:
63
Page 72
Example usage:
To configure a syslog host for all hosts:
delete syslog host
Purpose Used to remove a syslog host, that has been previously configured,
DES-3550:4#config syslog host 1 severity all facility local0
Command: config syslog host all severity all facility local0
Success.
DES-3550:4#
DES-3550:4#config syslog host all severity all facility local0
Command: config syslog host all severity all facility local0
Success.
DES-3550:4#
from the switch.
Syntax
Description
Parameters
Restrictions Only administrator-level users can issue this command.
Example usage:
To delete a previously configured syslog host:
delete syslog host [<index 1-4> | all]
The
delete syslog host
that has been previously configured from the switch.
<index 1-4> − Specifies that the command will be applied to an index
of hosts. There are four available indexes, numbered 1 through 4.
all − Specifies that the command will be applied to all hosts.
DES-3550:4#delete syslog host 4
Command: delete syslog host 4
Success.
DES-3550:4#
command is used to remove a syslog host
show syslog host
Purpose Used to display the syslog hosts currently configured on the switch.
Syntax
Description
show syslog host {<index 1-4>}
The
hosts that are currently configured on the switch.
show syslog host
command is used to display the syslog
64
Page 73
show syslog host
Example usage:
To show Syslog host information:
Parameters
Restrictions None.
DES-3550:4#show syslog host
Command: show syslog host
Syslog Global State: Disabled
Host Id Host IP Address Severity Facility UDP port Status
------- --------------- -------------- -------- -------- --------
1 10.1.1.2 All Local0 514 Disabled
2 10.40.2.3 All Local0 514 Disabled
3 10.21.13.1 All Local0 514 Disabled
Total Entries : 3
DES-3550:4#
<index 1-4> − Specifies that the command will be applied to an index
of hosts. There are four available indexes, numbered 1 through 4.
65
Page 74
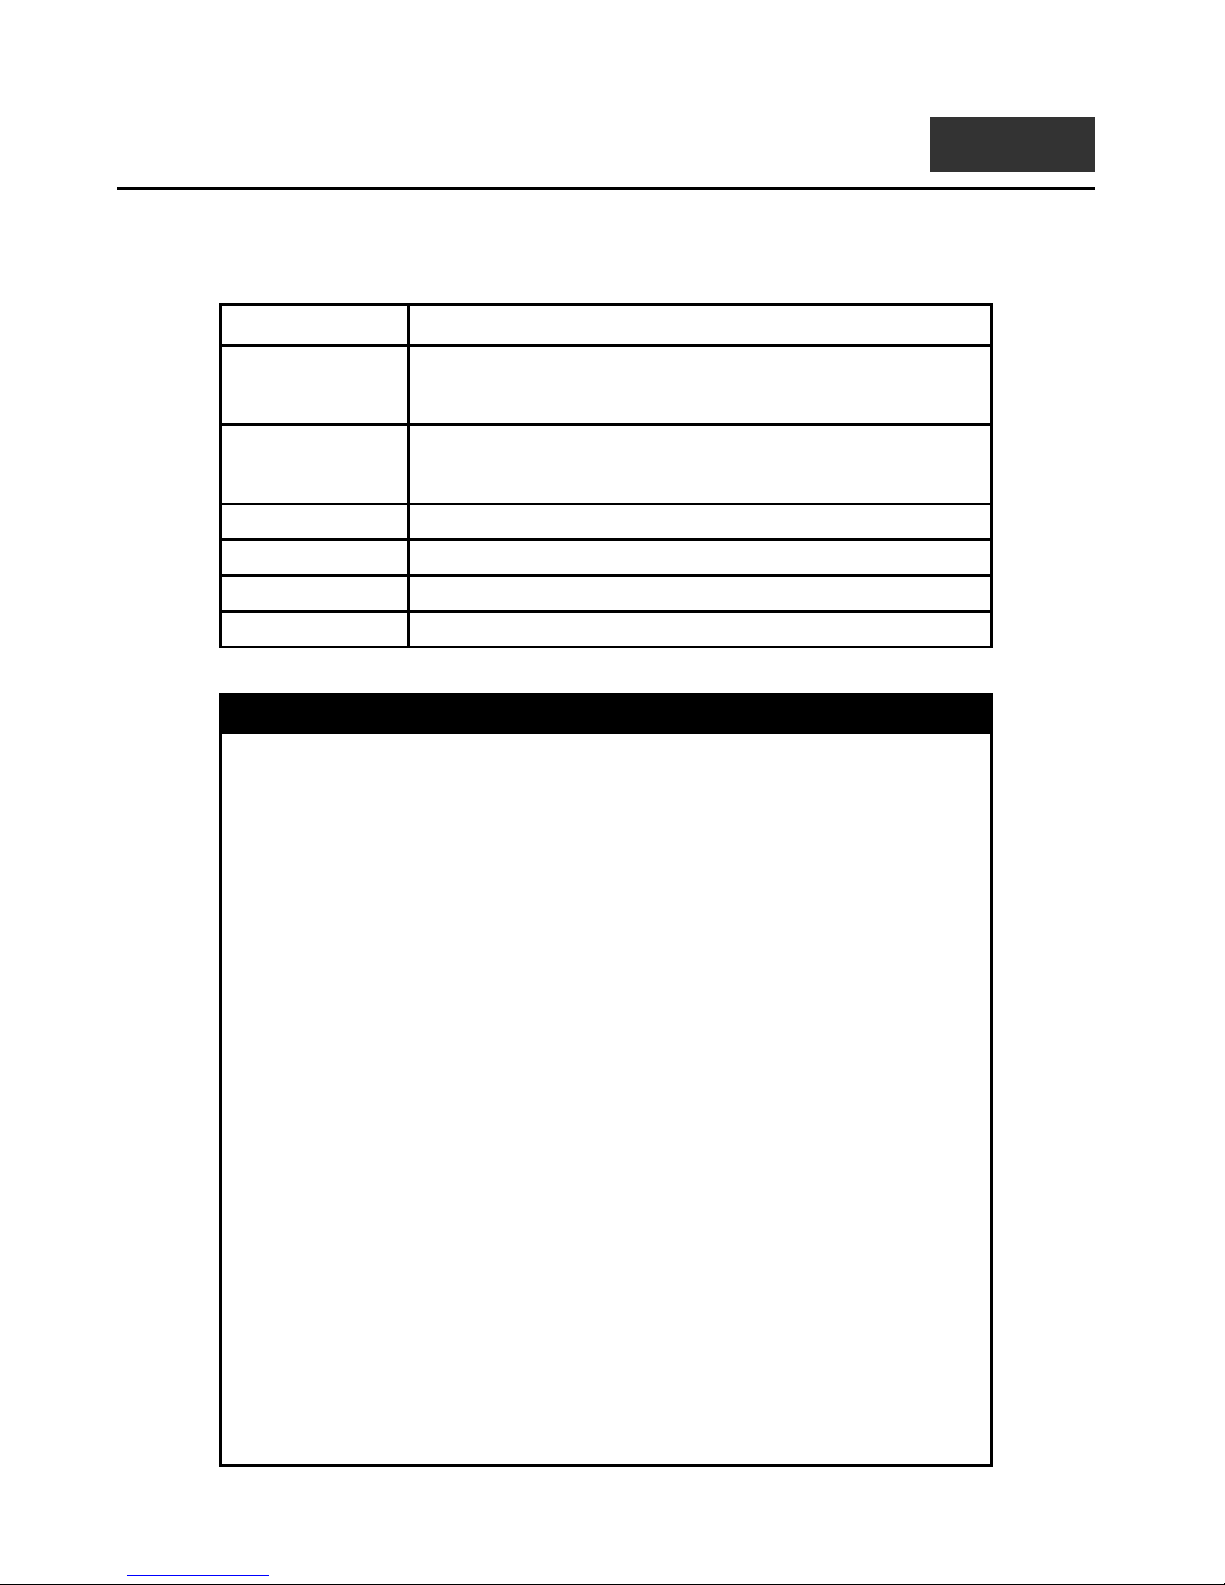
10
SPANNING TREE COMMANDS
The switch supports 802.1d STP and 802.1w Rapid STP. The spanning tree commands in the Command Line Interface (CLI)
are listed (along with the appropriate parameters) in the following table.
Command Parameters
config stp {maxage <value 6-40> | hellotime <value 1-10> | forwarddelay
<value 4-30> | priority <value 0-61440> | version [rstp | stp] |
txholdcount <value 1-10> | fbpdu [enable | disable]}
config stp ports [all | <portlist>] {cost [auto | <value 1-200000000>] | priority <value
0-240>|migrate [yes | no] |edge [true | false]|p2p [true | false | auto]
|state [enable | disable]}
enable stp
disable stp
show stp
show stp ports <portlist>
Each command is listed, in detail, in the following sections.
config stp
Purpose
Syntax
Description
Parameters
Used to setup STP and RSTP on the switch.
config stp {maxage <value 6-40> | hellotime <value 1-10> |
forwarddelay <value 4-30> | priority <value 0-61440> |
version[rstp | stp] | txholdcount <value 1-10>| fbpdu [enable |
disable]}
This command is used to setup the Spanning Tree Protocol (STP)
for the entire switch.
maxage <value> − The maximum amount of time (in seconds) that
the switch will wait to receive a BPDU packet before reconfiguring
STP. The user may choose a time between 6 and 40 seconds. The
default is 20 seconds.
hellotime <value> − The time interval between transmission of
configuration messages by the root device. The user may choose a
time between 1 and 10 seconds. The default is 2 seconds.
forwarddelay <value> − The maximum amount of time (in seconds)
that the root device will wait before changing states. The user may
choose a time between 4 and 30 seconds. The default is 15
seconds.
priority <value> − A numerical value between 0 and 61440 that is
used in determining the root device, root port, and designated port.
The device with the highest priority becomes the root device. The
lower the numerical value, the higher the priority. The default is
32,768.
version [rstp | stp] - select the Spanning Tree Protocol version used
for the switch.
66
Page 75
config stp
stp – Selct this parameter for IEEE 802.1d STP and for
•
IEEE 802.1w STP compatibility mode.
rstp - Select this paramter for IEEE 802.1w Rapid STP
•
mode.
txholdcount <1-10> - the maximum number of Hello packets
transmitted per interval. Default value = 3.
fbpdu [enable | disable] − Allows the forwarding of STP BPDU
packets from other network devices when STP is disabled on the
switch. The default is enabled.
Example usage:
To configure STP with maxage 18 and hellotime 4:
config stp ports
Purpose
Syntax
Description
Restrictions
Only administrator-level users can issue this command.
DES-3550:4#config stp maxage 18 hellotime 4
Command: config stp maxage 18 hellotime 4
Success.
DES-3550:4#
Used to setup STP on the port level.
config stp ports <portlist> {cost [auto | <value 1-200000000>] |
priority <value 0-240> | migrate [yes | no] | edge [true | false] |
p2p [true | false | auto]| state [enable | disable]
This command is used to create and configure STP for a group of
ports.
Parameters
cost<value> − This defines a metric that indicates the relative cost of
forwarding packets to the specified port list. Port cost can be set from
1 to 200000000. The lower the number, the greater the probability the
port will be chosen to forward packets.
Default port cost: 100Mbps port = 200000 Gigabit port = 20000
priority <value> − Port Priority can be from 0 to 240. The lower the
number, the greater the probability the port will be chosen as the Root
Port. Default = 128.
<portlist> − Specifies a port or range of ports to be configured.
migrate [yes | no] – yes will enable the port to migrate from 802.1d
STP status to 802.1w RSTP status. RSTP can coexist with standard
STP, however the benefits of RSTP are not realized on a port where
an 802.1d network connects to an 802.1w enabled network. Migration
should be enabled (yes) on ports connected to network stations or
segments that will be upgraded to 802.1w RSTP onall or some
67
Page 76
config stp ports
portion of the segment.
edge [true | false] – true designates the port as an edge port. Edge
ports cannot create loops, however an edge port can lose edge port
status if a topology change creates a potential for a loop. An edge
port normally should not receive BPDU packets. If a BPDU packet is
received it automatically loses edge port status. False indicates that
the port does not have edge port status.
p2p [true | false | auto] – true indicates a point-to-point (P2P) shared
link. P2P ports are similar to edge ports however they are restricted in
that a P2P port must operate in full-duplex. Like edge ports, P2P
ports transition to a forwarding state rapidly thus benefiting from
RSTP. A p2p value of false indicates that the port cannot have p2p
status.
and operate as if the p2p status were
this status (for example if the port is forced to half-duplex operation)
the p2p status changes to operate as if the p2p value were
state [enable | disable] − Allows STP to be enabled or disabled for the
ports specified in the port list. The default is disabled.
Restrictions Only administrator-level users can issue this command.
allows the port to have p2p status whenever possible
Auto
. If the port cannot maintain
true
false
.
Example usage:
To configure STP with path cost 19, priority 16, and state enabled for ports 1-5 of the switch.
DES-3550:4#config stp ports 1-5 cost 19 priority 16 state enabled
Command: config stp ports 1-5 cost 19 priority 16 state enabled
Success.
DES-3550:4#
enable stp
Purpose Used to globally enable STP on the switch.
Syntax
Description This command allows the Spanning Tree Protocol to be globally
Parameters None.
Restrictions Only administrator-level users can issue this command.
enable stp
enabled on the switch.
Example usage:
To enable STP, globally, on the switch:
68
Page 77
DES-3550:4#enable stp
Command: enable stp
Success.
DES-3550:4#
disable stp
Purpose Used to globally disable STP on the switch.
Example usage:
To disable STP on the switch:
Syntax
Description This command allows the Spanning Tree Protocol to be globally
Parameters None.
Restrictions Only administrator-level users can issue this command.
disable stp
disabled on the switch.
DES-3550:4#disable stp
Command: disable stp
Success.
DES-3550:4#
show stp
Purpose Used to display the switch’s current STP configuration.
Syntax
Description This command displays the switch’s current STP configuration.
Parameters none
Restrictions None.
Example usage:
To display the status of STP on the switch:
Status 1: STP enabled with STP compatible version
show stp
69
Page 78
DES-3550:4#show stp
Command: show stp
Bridge Parameters Settings
STP Status : Enabled
Max Age : 20
Hello Time : 2
Forward Delay : 15
Priority : 32768
STP Version : RSTP
TX Hold Count : 3
Forwarding BPDU : Enabled
Designated Root Bridge : 00-00-51-43-70-00
Root Priority : 32768
Cost to Root : 200000
Root Port : 10
Last Topology Change : 53sec
Topology Changes Count : 1
Protocol Specification : 3
Max Age : 20
Hello Time : 2
Forward Delay : 15
Hold Time : 3
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
Status 2 : STP disabled
DES-3550:4#show stp
Command: show stp
Bridge Parameters Settings
STP Status : Disabled
Max Age : 20
Hello Time : 2
Forward Delay : 15
Priority : 32768
STP Version : STP compatible
TX Hold Count : 3
Forwarding BPDU : Enabled
DES-3550:4#
show stp ports
Purpose Used to display the switch’s current per-port group STP
configuration.
Syntax
show stp ports <portlist>
70
Page 79
show stp ports
Description This command displays the switch’s current per-port group STP
configuration.
Example usage:
To display STP state of port 1-9 of module 1:
DES-3550:4#show stp ports
Command: show ports
Port Designated Bridge State Cost Pri Edge P2P Status Role
------ ------------------ ---- ---------- ---- ---- --- ---------- ----------
1 N/A Yes *200000 128 No Yes Disabled Disabled
2 N/A Yes *200000 128 No Yes Disabled Disabled
3 N/A Yes *200000 128 No Yes Disabled Disabled
4 N/A Yes *200000 128 No Yes Disabled Disabled
5 N/A Yes *200000 128 No Yes Disabled Disabled
6 N/A Yes *200000 128 No Yes Disabled Disabled
7 N/A Yes *200000 128 No Yes Disabled Disabled
8 N/A Yes *200000 128 No Yes Disabled Disabled
9 N/A Yes *200000 128 No Yes Disabled Disabled
10 8000/000102030400 Yes *200000 128 No Yes Forwarding Designated
11 N/A Yes *200000 128 No Yes Disabled Disabled
12 N/A Yes *200000 128 No Yes Disabled Disabled
13 N/A Yes *200000 128 No Yes Disabled Disabled
14 N/A Yes *200000 128 No Yes Disabled Disabled
15 N/A Yes *200000 128 No Yes Disabled Disabled
16 N/A Yes *200000 128 No Yes Disabled Disabled
17 N/A Yes *200000 128 No Yes Disabled Disabled
18 N/A Yes *200000 128 No Yes Disabled Disabled
19 N/A Yes *200000 128 No Yes Disabled Disabled
20 N/A Yes *200000 128 No Yes Disabled Disabled
21 N/A Yes *200000 128 No Yes Disabled Disabled
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
Parameters
Restrictions
<portlist> − Specifies a port or range of ports to be displayed.
None
71
Page 80
11
FORWARDING DATABASE COMMANDS
The layer 2 forwarding database commands in the Command Line Interface (CLI) are listed (along with the appropriate
parameters) in the following table.
Command Parameters
create fdb <vlan_name 32> <macaddr> port <port>
create multicast_fdb <vlan_name 32> <macaddr>
config multicast_fdb <vlan_name 32> <macaddr> [add | delete] <portlist>
config fdb aging_time <sec 10-1000000>
delete fdb <vlan_name 32> <macaddr>
clear fdb [vlan <vlan_name 32> | port <port> | all]
show multicast_fdb {vlan <vlan_name 32> | mac_address <macaddr>}
show fdb {port <port> | vlan <vlan_name 32> | mac_address
<macaddr> | static | aging_time}
config multicast
port_filtering_mode
show multicast
port_filtering_mode
Each command is listed, in detail, in the following sections.
[<portlist> | all] [forward_all_groups |
forward_unregistered_groups | filter_unregistered_groups]
{<portlist>}
create fdb
Purpose Used to create a static entry to the unicast MAC address forwarding
table (database)
Syntax
Description This command will make an entry into the switch’s unicast MAC
Parameters
create fdb <vlan_name 32> <macaddr> port <port>
address forwarding database.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<macaddr> − The MAC address that will be added to the forwarding
table.
<port> − The port number corresponding to the MAC destination
address. The switch will always forward traffic to the specified device
through this port.
Restrictions Only administrator-level users can issue this command.
Example usage:
To create a unicast MAC FDB entry:
72
Page 81
DES-3550:4#create fdb default 00-00-00-00-01-02 port 5
Command: create fdb default 00-00-00-00-01-02 port 5
Success.
DES-3550:4#
create multicast_fdb
Purpose Used to create a static entry to the multicast MAC address
forwarding table (database)
Example usage:
To create multicast MAC forwarding:
Syntax
Description This command will make an entry into the switch’s multicast MAC
Parameters
Restrictions Only administrator-level users can issue this command.
DES-3550:4#create multicast_fdb default 01-00-00-00-00-01
Command: create multicast_fdb default 01-00-00-00-00-01
Success.
DES-3550:4#
create multicast_fdb <vlan_name 32> <macaddr>
address forwarding database.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<macaddr> − The MAC address that will be added to the forwarding
table.
config multicast_fdb
Purpose Used to configure the switch’s multicast MAC address forwarding
Syntax
Description This command configures the multicast MAC address forwarding
Parameters
database.
config multicast_fdb <vlan_name 32> <macaddr> [add | delete]
<portlist>
table.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<macaddr> − The MAC address that will be added to the multicast
forwarding table.
[add | delete] − Add will add ports to the forwarding table. Delete will
remove ports from the multicast forwarding table.
73
Page 82
config multicast_fdb
<portlist> − Specifies a range of ports to be configured.
Example usage:
To add multicast MAC forwarding:
Restrictions
DES-3550:4#config multicast_fdb default 01-00-00-00-00-01 add
1-5
Command: config multicast_fdb default 01-00-00-00-00-01 add 11-5
Success.
DES-3550:4#
Only administrator-level users can issue this command.
config fdb aging_time
Purpose Used to set the aging time of the forwarding database.
Syntax
Description The aging time affects the learning process of the switch. Dynamic
config fdb aging_time <sec 10-1000000>
forwarding table entries, which are made up of the source MAC
addresses and their associated port numbers, are deleted from the
table if they are not accessed within the aging time. The aging time
can be from 10 to 1000000 seconds with a default value of 300
seconds. A very long aging time can result in dynamic forwarding
table entries that are out-of-date or no longer exist. This may cause
incorrect packet forwarding decisions by the switch. If the aging time
is too short however, many entries may be aged out too soon. This
will result in a high percentage of received packets whose source
addresses cannot be found in the forwarding table, in which case the
switch will broadcast the packet to all ports, negating many of the
benefits of having a switch.
Parameters
Restrictions
Example usage:
To set the fdb aging time:
<sec> − The aging time for the MAC address forwarding database
value. The value in seconds may be between 10 and 1000000
seconds.
Only administrator-level users can issue this command.
DES-3550:4#config fdb aging_time 300
Command: config fdb aging_time 300
Success.
DES-3550:4#
74
Page 83
delete fdb
Purpose Used to delete an entry to the switch’s forwarding database.
Example usage:
To delete a permanent FDB entry:
Example usage:
Syntax
Description This command is used to delete a previous entry to the switch’s
Parameters
Restrictions Only administrator-level users can issue this command.
delete fdb <vlan_name 32> <macaddr>
MAC address forwarding database.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<macaddr> − The MAC address that will be added to the forwarding
table.
DES-3550:4#delete fdb default 00-00-00-00-01-02
Command: delete fdb default 00-00-00-00-01-02
Success.
DES-3550:4#
To delete a multicast fdb entry:
DES-3550:4#delete fdb default 01-00-00-00-01-02
Command: delete fdb default 01-00-00-00-01-02
Success.
DES-3550:4#
clear fdb
Purpose Used to clear the switch’s forwarding database of all dynamically
learned MAC addresses.
Syntax
Description This command is used to clear dynamically learned entries to the
Parameters
clear fdb [vlan <vlan_name 32> | port <port> | all]
switch’s forwarding database.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<port> − The port number corresponding to the MAC destination
address. The switch will always forward traffic to the specified device
75
Page 84
clear fdb
Restrictions Only administrator-level users can issue this command.
Example usage:
To clear all FDB dynamic entries:
show multicast_fdb
Purpose Used to display the contents of the switch’s multicast forwarding
Syntax
Description This command is used to display the current contents of the switch’s
Parameters
Restrictions None.
through this port.
all − Clears all dynamic entries to the switch’s forwarding database.
DES-3550:4#clear fdb all
Command: clear fdb all
Success.
DES-3550:4#
database.
show mulitcast_fdb [vlan <vlan_name 32> | mac_address
<macaddr>]
multicast MAC address forwarding database.
<vlan_name 32> − The name of the VLAN on which the MAC address
resides.
<macaddr> − The MAC address that is present in the forwarding
database table.
Example usage:
To display multicast MAC address table:
DES-3550:4#show multicast_fdb vlan default
Command: show multicast_fdb vlan default
VLAN Name : default
MAC Address : 01-00-5E-00-00-00
Egress Ports : 1-5
Mode : Static
Total Entries : 1
DES-3550:4#
76
Page 85
show fdb
Purpose Used to display the current unicast MAC address forwarding
database.
Syntax
Description This command will display the current contents of the switch’s
Parameters
Restrictions
Example usage:
To display unicast MAC address table:
show fdb {port <port> | vlan <vlan_name 32> | mac_address
<macaddr> | static | aging_time}
forwarding database.
<port> − The port number corresponding to the MAC destination
address. The switch will always forward traffic to the specified device
through this port.
<vlan_name 32> − The name of the VLAN on which the MAC
address resides.
<macaddr> − The MAC address that is present in the forwarding
database table.
static − Displays the static MAC address entries.
aging_time − Displays the aging time for the MAC address forwarding
database.
None.
DES-3550:4#show fdb
Command: show fdb
Unicast MAC Address Aging Time = 300
VID VLAN Name MAC Address Port Type
---- ---------------- ----------------- ------ ---------------1 default 00-00-39-34-66-9A 10 Dynamic
1 default 00-00-51-43-70-00 10 Dynamic
1 default 00-00-5E-00-01-01 10 Dynamic
1 default 00-00-74-60-72-2D 10 Dynamic
1 default 00-00-81-05-00-80 10 Dynamic
1 default 00-00-81-05-02-00 10 Dynamic
1 default 00-00-81-48-70-01 10 Dynamic
1 default 00-00-E2-4F-57-03 10 Dynamic
1 default 00-00-E2-61-53-18 10 Dynamic
1 default 00-00-E2-6B-BC-F6 10 Dynamic
1 default 00-00-E2-7F-6B-53 10 Dynamic
1 default 00-00-E2-82-7D-90 10 Dynamic
1 default 00-00-F8-7C-1C-29 10 Dynamic
1 default 00-01-02-03-04-00 CPU Self
1 default 00-01-02-03-04-05 10 Dynamic
1 default 00-01-30-10-2C-C7 10 Dynamic
1 default 00-01-30-FA-5F-00 10 Dynamic
1 default 00-02-3F-63-DD-68 10 Dynamic
CTRL+C ESC q Quit SPACE n Next Page ENTER Next Entry a All
77
Page 86
config multicast port_filtering_mode
Purpose Used to configure the multicast packet filtering mode on a port per
port basis.
Syntax
Description This command will configure the multicast packet filtering mode for
Parameters <portlist> Specifies a port or range of ports to view.
Restrictions
Example usage:
To configure the multicast filtering mode to forward all groups on ports 1 through 4.
config multicast port_filtering_mode [<portlist> | all]
[forward_all_groups | forward_unregistered_groups |
filter_unregistered_groups]
specified ports on the switch.
[forward_all_groups | forward_unregistered_groups |
filter_unregistered_groups] – The user may set the filtering mode to
any of these three options
Only administrator-level users can issue this command.
DES-3550:4#config multicast port_filtering_mode 1-4
forward_all_groups
Command: config multicast port_filtering_mode 1-4
forward_all_groups
Success.
DES-3550:4#
Example usage:
To view the multicast port filtering mode for all ports:
show multicast port_filtering_mode
Purpose Used to show the multicast packet filtering mode on a port per port
basis.
Syntax
Description This command will display the current multicast packet filtering mode
Parameters <portlist> Specifies a port or range of ports to view.
Restrictions
show multicast port_filtering_mode {<portlist>}
for specified ports on the switch.
None.
78
Page 87
DES-3550:4#show multicast port_filtering_mode
Command: show multicast port_filtering_mode
Port Multicast Filter Mode
------ ---------------------------
1 forward_unregistered_groups
2 forward_unregistered_groups
3 forward_unregistered_groups
4 forward_unregistered_groups
5 forward_unregistered_groups
6 forward_unregistered_groups
7 forward_unregistered_groups
8 forward_unregistered_groups
9 forward_unregistered_groups
10 forward_unregistered_groups
11 forward_unregistered_groups
12 forward_unregistered_groups
13 forward_unregistered_groups
14 forward_unregistered_groups
15 forward_unregistered_groups
16 forward_unregistered_groups
17 forward_unregistered_groups
18 forward_unregistered_groups
19 forward_unregistered_groups
20 forward_unregistered_groups
CTRL+C ESC q Quit SPACE n Next Page p Previous Page r Refresh
79
Page 88
12
BROADCAST STORM CONTROL COMMANDS
The broadcast storm control commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters)
in the following table.
Command Parameters
config traffic control [<storm_grouplist 1-8> | all ] { broadcast [enabled | disabled] |
multicast [enabled | disabled] | dlf [enabled | disabled] | threshold
<value 0-255> }
show traffic control group_list <storm_grouplist>
Each command is listed, in detail, in the following sections.
config traffic control
Purpose Used to configure broadcast/multicast traffic control.
Syntax
Description This command is used to configure broadcast storm control.
Parameters
Restrictions Only administrator-level users can issue this command.
config traffic control [<storm_grouplist 1-8> | all] broadcast
[enable | disable] | multicast [enable | disable] | dlf [enable |
disable] | threshold <value 0-255>
<storm_grouplist> − Used to specify a broadcast storm control
group. This is specified by entering the syntax unit_id.
all − Specifies all broadcast storm control groups on the switch.
broadcast [enable | disable] − Enables or disables broadcast storm
control.
multicast [enable | disable] − Enables or disables multicast storm
control.
dlf [enable | disable] − Enables or disables dlf traffic control.
threshold <value> − The upper threshold at which the specified
traffic control is switched on. The <value> is the number of
broadcast/multicast/dlf packets, in Kbps, received by the switch that
will trigger the storm traffic control measures.
Example usage:
To configure traffic control and enable broadcast storm control system wide:
DES-3550:4#config traffic control all broadcast enabled
Command: config traffic control all broadcast enabled
Success.
DES-3550:4#
80
Page 89
show traffic control
Purpose Used to display current traffic control settings.
Example usage:
To display traffic control setting:
Syntax
Description This command displays the current storm traffic control configuration
Parameters
Restrictions None.
DES-3550:4#show traffic control
Command: show traffic control
Traffic Control
Broadcast Multicast
Destination
Module Group [ports] Threshold Storm Storm Lookup
Fail
------ ------------- --------- --------- --------- --------
1 1 [1-8] 128 Disabled Disabled Disabled
1 2 [9-16] 128 Disabled Disabled Disabled
1 3 [17-24] 128 Disabled Disabled Disabled
1 4 [25-32] 128 Disabled Disabled Disabled
1 5 [33-40] 128 Disabled Disabled Disabled
1 6 [41-48] 128 Disabled Disabled Disabled
1 7 [49] 128 Disabled Disabled Disabled
1 8 [50] 128 Disabled Disabled Disabled
Total Entries: 8
DES-3550:4#
show traffic control {group_list <storm_grouplist>}
on the switch.
group_list <storm_grouplist> − Used to specify a broadcast storm
control group. This is specified by entering the syntax unit_id.
81
Page 90
13
QOS COMMANDS
The DES-3550 switch supports 802.1p priority queuing. The switch has 4 priority queues. These priority queues are numbered
from 3 (Class 3) — the highest priority queue — to 0 (Class 0) — the lowest priority queue. The eight priority tags specified in
IEEE 802.1p (p0 to p7) are mapped to the switch’s priority queues as follows:
• Priority 0 is assigned to the Switch’s Q1 queue.
Priority 1 is assigned to the Switch’s Q0 queue.
•
• Priority 2 is assigned to the Switch’s Q0 queue.
• Priority 3 is assigned to the Switch’s Q1 queue.
• Priority 4 is assigned to the Switch’s Q2 queue.
• Priority 5 is assigned to the Switch’s Q2 queue.
• Priority 6 is assigned to the Switch’s Q3 queue.
• Priority 7 is assigned to the Switch’s Q3 queue.
Priority scheduling is implemented by the priority queues stated above. The switch will empty the four hardware priority queues
in order, beginning with the highest priority queue, 4, to the lowest priority queue, 0. Each hardware queue will transmit all of
the packets in its buffer before permitting the next lower priority to transmit its packets. When the lowest hardware priority
queue has finished transmitting all of its packets, the highest hardware priority queue will begin transmitting any packets it may
have received.
The commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in the following table.
Command Parameters
config
bandwidth_control
show bandwidth_control <portlist>
config scheduling <class_id 0-3> {max_packet <value 0-255> | max_latency
show scheduling
config 802.1p
user_priority
show 802.1p
user_priority
config 802.1p
default_priority
show 802.1p
default_priority
Each command is listed, in detail, in the following sections.
[<portlist>] {rx_rate [no_limit | <value 1-1000>] | tx_rate
[no_limit<value 1-1000>]}
<value 0-255>}
<priority 0-7>
<class_id 0-3>
[<portlist> |all ] <priority 0-7>
<portlist>
config bandwidth_control
Purpose Used to configure bandwidth control on a by-port basis.
Syntax
Description
config bandwidth_control [<portlist>] {rx_rate [no_limit | <value
1-1000>] | tx_rate [no_limit <value 1-1000>]}
The
config bandwidth_control
82
command is used to configure
Page 91
config bandwidth_control
bandwidth on a by-port basis.
Parameters
Restrictions Only administrator-level users can issue this command.
<portlist> − Specifies a port or range of ports to be configured.
rx_rate − Specifies that one of the parameters below (
<value 1-1000>
specified ports will be allowed to receive packets
tx_rate − Specifies that one of the parameters below (
<value 1-1000>
specified ports will be allowed to transmit packets.
The transfer(tx) and receive(rx) rate of packets for Gigabit ports
must be configured in a multiple of 8 Mbits. (8, 16, 24…)
) will be applied to the rate at which the above
no_limit − Specifies that there will be no limit on the rate of
packets received by the above specified ports.
<value 1-1000> − Specifies the packet limit, in Mbps, that
the above ports will be allowed to receive.
) will be applied to the rate at which the above
no_limit − Specifies that there will be no limit on the rate of
packets received by the above specified ports.
<value 1-1000> − Specifies the packet limit, in Mbps, that
the above ports will be allowed to receive.
no_limit
no_limit
or
or
Example usage:
To configure bandwidth control:
DES-3550:4#config bandwidth_control 1-10 tx_rate 10
Command: config bandwidth_control 1-10 tx_rate 10
Success.
DES-3550:4#
show bandwidth_control
Purpose Used to display the bandwidth control table.
Syntax
Description
Parameters
Restrictions None.
show bandwidth_control {<portlist>}
The
show bandwidth_control
bandwidth control configuration on the switch, on a port-by-port
basis.
<portlist> − Specifies a port or range of ports to be viewed.
command displays the current
Example usage:
83
Page 92
To display bandwidth control settings:
DES-3550:4#show bandwidth_control 1-10
Command: show bandwidth_control 1-10
Bandwidth Control Table
Port RX Rate (Mbit/sec) TX_RATE (Mbit/sec)
---- ------------------------ ----------------------
1:1 no_limit 10
1:2 no_limit 10
1:3 no_limit 10
1:4 no_limit 10
1:5 no_limit 10
1:6 no_limit 10
1:7 no_limit 10
1:8 no_limit 10
1:9 no_limit 10
1:10 no_limit 10
DES-3550:4#
config scheduling
Purpose Used to configure the traffic scheduling mechanism for each COS
queue.
Syntax
Description The switch contains 4 hardware priority queues. Incoming packets
config scheduling <class_id 0-3> [max_packet <value 0255>|max_latency <value 0-255>]
must be mapped to one of these four queues. This command is
used to specify the rotation by which these four hardware priority
queues are emptied.
The switch’s default (if the config scheduling command is not used,
or if the config scheduling command is entered with both max_packet
and max_latency parameters are set to 0) is to empty the 4 hardware
priority queues in order − from the highest priority queue (hardware
queue 3) to the lowest priority queue (hardware queue 0). Each
hardware queue will transmit all of the packets in its buffer before
allowing the next lower priority queue to transmit its packets. When
the lowest hardware priority queue has finished transmitting all of its
packets, the highest hardware priority queue can again transmit any
packets it may have received.
The max_packets parameter allows you to specify the maximum
number of packets a given hardware priority queue can transmit
before allowing the next lowest hardware priority queue to begin
transmitting its packets. A value between 0 and 255 can be specified.
For example, if a value of 3 is specified, then the highest hardware
priority queue (number 3) will be allowed to transmit 3 packets − then
the next lowest hardware priority queue (number 2) will be allowed to
transmit 3 packets, and so on, until all of the queues have
84
Page 93
config scheduling
transmitted 3 packets. The process will then repeat.
The max_latency parameter allows you to specify the maximum
amount of time that packets are delayed before being transmitted to
a given hardware priority queue. A value between 0 and 255 can be
specified. This number is then multiplied by 16 ms to determine the
maximum latency. For example, if 3 is specified, the maximum
latency allowed will be 3 X 16 = 48 ms.
When the specified hardware priority queue has been waiting to
transmit packets for this amount of time, the current queue will finish
transmitting its current packet, and then allow the hardware priority
queue whose max_latency timer has expired to begin transmitting
packets.
Parameters
Restrictions Only administrator-level users can issue this command.
<class_id 0-3> − This specifies which of the four hardware priority
queues the config scheduling command will apply to. The four
hardware priority queues are identified by number − from 0 to 3 −
with the 0 queue being the lowest priority.
max_packet <value 0-255> − Specifies the maximum number of
packets the above specified hardware priority queue will be allowed
to transmit before allowing the next lowest priority queue to transmit
its packets. A value between 0 and 255 can be specified.
max_latency <value 0-255> − Specifies the maximum amount of time
the above specified hardware priority queue will be allowed to
transmit packets before allowing the next lowest hardware priority
queue to begin transmitting its packets. A value between 0 and 255
can be specified − with this value multiplied by 16 ms to arrive at the
total allowed time for the queue to transmit packets. For example, a
value of 3 specifies 3 X 16 = 48 ms. The queue will continue
transmitting the last packet until it is finished when the max_latency
timer expires.
Example usage:
To configure the traffic scheduling mechanism for each queue:
DES-3550:4# config scheduling 0 max_packet 100
max_latency 150
Command: config scheduling 0 max_packet 100
max_latency 150
Success.
DES-3550:4#
show scheduling
Purpose Used to display the currently configured traffic scheduling on the
switch.
Syntax
Description
show scheduling
The
show scheduling
scheduling mechanisms in use on the switch.
command will display the current traffic
85
Page 94
show scheduling
Parameters None.
Example usage:
To display the current scheduling configuration:
Restrictions
None.
DES-3550:4# show scheduling
Command: show scheduling
QOS Output Scheduling
Class ID MAX. Packets MAX. Latency
------------ ------------------- --------------------
Class-0 100 150
Class-1 99 100
Class-2 91 101
Class-3 21 201
DES-3550:4#
config 802.1p user_priority
Purpose Used to map the 802.1p user priority of an incoming packet to one of
the four hardware queues available on the switch.
Syntax
Description This command allows you to configure the way the switch will map
config 802.1p user_priority <priority 0-7> <class_id 0-3>
an incoming packet, based on its 802.1p user priority, to one of the
four available hardware priority queues on the switch.
The switch’s default is to map the following incoming 802.1p user
priority values to the four hardware priority queues:
802.1p Hardware Queue Remark
0 1 Mid-low
1 0 Lowest
2 0 Lowest
3 1 Mid-low
4 2 Mid-high
5 2 Mid-high
6 3 Highest
7 3 Highest.
This mapping scheme is based upon recommendations contained in
IEEE 802.1D.
You can change this mapping by specifying the 802.1p user priority
you want to go to the <class_id 0-3> (the number of the hardware
86
Page 95
Example usage:
To configure 802.1 user priority on the switch:
config 802.1p user_priority
queue).
Restrictions Only administrator-level users can issue this command.
<priority 0-7> − The 802.1p user priority you want to associate with
the <class_id 0-3> (the number of the hardware queue) with.
<class_id 0-3> − The number of the switch’s hardware priority queue.
The switch has four hardware priority queues available. They are
numbered between 0 (the lowest priority) and 3 (the highest priority).
DES-3550:4# config 802.1p user_priority 1 3
Command: config 802.1p user_priority 1 3
Success.
DES-3550:4#
Example usage:
To show 802.1p user priority:
show 802.1p user_priority
Purpose Used to display the current mapping between an incoming packet’s
802.1p priority value and one of the switch’s four hardware priority
queues.
Syntax
Description
Parameters None.
Restrictions None.
show 802.1p user_priority
The
show 802.1p user_priority
mapping of an incoming packet’s 802.1p priority value to one of the
switch’s four hardware priority queues.
DES-3550:4# show 802.1p user_priority
Command: show 802.1p user_priority
QOS Class of Traffic
Priority-0 -> <Class-1>
Priority-1 -> <Class-0>
Priority-2 -> <Class-0>
Priority-3 -> <Class-1>
Priority-4 -> <Class-2>
Priority-5 -> <Class-2>
Priority-6 -> <Class-3>
Priority-7 -> <Class-3>
DES-3550:4#
command displays the current
87
Page 96
config 802.1p default_priority
Example usage:
To configure 802.1p default priority on the switch:
Purpose
Syntax
Description
Parameters
Restrictions
Used to configure the 802.1p default priority settings on the switch.
If an untagged packet is received by the switch, the priority
configured with this command will be written to the packet’s priority
field.
config 802.1p default_priority [<portlist> | all] <priority 0-7>
This command allows you to specify default priority handling of
untagged packets received by the switch. The priority value entered
with this command will be used to determine which of the four
hardware priority queues the packet is forwarded to.
<portlist> − Specifies a port or range of ports to be configured.
all − Specifies that the command applies to all ports on the switch.
<priority 0-7> − The priority value you want to assign to untagged
packets received by the switch or a range of ports on the switch.
Only administrator-level users can issue this command.
DES-3550:4#config 802.1p default_priority all 5
Command: config 802.1p default_priority all 5
Success.
DES-3550:4#
Example usage:
To display the current 802.1p default priority configuration on the switch:
show 802.1 default_priority
Purpose Used to display the currently configured 802.1p priority value that will
be assigned to an incoming, untagged packet before being
forwarded to its destination.
Syntax
Description
Parameters
Restrictions None.
show 802.1p default_priority {<portlist>}
The
show 802.1p default_priority
configured 802.1p priority value that will be assigned to an incoming,
untagged packet before being forwarded to its destination.
<portlist> − Specifies a port or range of ports to be configured.
88
command displays the currently
Page 97
DES-3550:4# show 802.1p default_priority
Command: show 802.1p default_priority
Port Priority
------- ----------1 0
2 0
3 0
4 0
5 0
6 0
7 0
8 0
9 0
10 0
11 0
12 0
13 0
14 0
15 0
16 0
17 0
18 0
19 0
20 0
CTRL+C ESC q Quit Space n Next Page Enter Next Entry a All
89
Page 98
14
PORT MIRRORING COMMANDS
The port mirroring commands in the Command Line Interface (CLI) are listed (along with the appropriate parameters) in the
following table.
Command Parameters
config mirror port <port> [add | delete] source ports <portlist> [rx | tx | both]
enable mirror
disable mirror
show mirror
Each command is listed, in detail, in the following sections.
config mirror port
Purpose
Syntax
Description This command allows a range of ports to have all of their traffic also
Parameters
Used to configure a mirror port − source port pair on the switch.
Traffic from any source port to a target port can be mirrored for realtime analysis. A logic analyzer or an RMON proble can then be
attached to study the traffic crossing the source port in a completely
obtrusive manner.
config mirror port <port> add source ports <portlist> [rx | tx |
both]
sent to a designated port, where a network sniffer or other device
can monitor the network traffic. In addition, you can specify that only
traffic received by or sent by one or both is mirrored to the Target
port.
<port> − This specifies the Target port (the port where mirrored
packets will be received). The target port must be configured in the
same VLAN and must be operationg at the same speed a s the
source port. If the target port is operating at a lower speed, the
source port will be forced to drop its operating speed to match that of
the target port.
source ports – The port or ports being mirrored. This cannot include
the Target port.
<portlist> − This specifies a range of ports that will be mirrored. That
is, the range of ports in which all traffic will be copied and sent to the
Target port.
rx − Allows the mirroring of only packets received by (flowing into) the
port or ports in the port list.
tx − Allows the mirroring of only packets sent to (flowing out of) the
port or ports in the port list.
both − Mirrors all the packets received or sent by the port or ports in
the port list.
Restrictions
The Target port cannot be listed as a source port. Only administrator-
90
Page 99
Example usage:
To add the mirroring ports:
config mirror port
level users can issue this command.
DES-3550:4# config mirror port 1 add source ports 2-7 both
Command: config mirror port 1 add source ports 2-7 both
Success.
DES-3550:4#
config mirror delete
Purpose Used to delete a port mirroring configuration|
Example usage:
Syntax
Description This command is used to delete a previously entered port mirroring
Parameters
Restrictions Only administrator-level users can issue this command.
config mirror port <port> delete source port <portlist> [rx | tx |
both]
configuration.
<port> − This specifies the Target port (the port where mirrored
packets will be received).
<portlist> − This specifies a range of ports that will be mirrored. That
is, the range of ports in which all traffic will be copied and sent to the
Target port.
rx − Allows the mirroring of only packets received by (flowing into)
the port or ports in the port list.
tx − Allows the mirroring of only packets sent to (flowing out of) the
port or ports in the port list.
both − Mirrors all the packets received or sent by the port or ports in
the port list.
To delete the mirroring ports:
DES-3550:4#config mirror port 1 delete source port 2-4
Command: config mirror 1 delete source 2-4
Success.
DES-3550:4#
91
Page 100
enable mirror
Purpose Used to enable a previously entered port mirroring configuration.
Example usage:
To enable mirroring configurations:
Syntax
Description
Parameters None.
Restrictions Only administrator-level users can issue this command.
enable mirror
This command, combined with
allows you to enter a port mirroring configuration into the switch, and
then turn the port mirroring on and off without having to modify the
port mirroring configuration.
DES-3550:4#enable mirror
Command: enable mirror
Success.
DES-3550:4#
the disable mirror
command below,
disable mirror
Example usage:
To disable mirroring configurations:
Purpose Used to disable a previously entered port mirroring configuration.
Syntax
Description
Parameters None.
Restrictions Only administrator-level users can issue this command.
DES-3550:4#disable mirror
Command: disable mirror
Success.
DES-3550:4#
disable mirror
This command, combined with
allows you to enter a port mirroring configuration into the switch, and
then turn the port mirroring on and off without having to modify the
port mirroring configuration.
the enable mirror
command above,
92
 Loading...