

Page 1
HUAWEI NetEngine80E/40E Router
V600R003C00
Configuration Guide - Basic
Configurations
Issue 02
Date 2011-09-10
HUAWEI TECHNOLOGIES CO., LTD.
Page 2
Copyright © Huawei Technologies Co., Ltd. 2011. All rights reserved.
No part of this document may be reproduced or transmitted in any form or by any means without prior written
consent of Huawei Technologies Co., Ltd.
Trademarks and Permissions
and other Huawei trademarks are trademarks of Huawei Technologies Co., Ltd.
All other trademarks and trade names mentioned in this document are the property of their respective holders.
Notice
The purchased products, services and features are stipulated by the contract made between Huawei and the
customer. All or part of the products, services and features described in this document may not be within the
purchase scope or the usage scope. Unless otherwise specified in the contract, all statements, information,
and recommendations in this document are provided "AS IS" without warranties, guarantees or representations
of any kind, either express or implied.
The information in this document is subject to change without notice. Every effort has been made in the
preparation of this document to ensure accuracy of the contents, but all statements, information, and
recommendations in this document do not constitute the warranty of any kind, express or implied.
Huawei Technologies Co., Ltd.
Address: Huawei Industrial Base
Bantian, Longgang
Shenzhen 518129
People's Republic of China
Website: http://www.huawei.com
Email: [email protected]
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
i
Page 3
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations About This Document
About This Document
Purpose
This part describes the organization of this document, product version, intended audience,
conventions, and Change history.
NOTE
l This document takes interface numbers and link types of the NE40E-X8 as an example. In working
situations, the actual interface numbers and link types may be different from those used in this
document.
l On NE80E/40E series excluding NE40E-X1 and NE40E-X2, line processing boards are called Line
Processing Units (LPUs) and switching fabric boards are called Switching Fabric Units (SFUs). On
the NE40E-X1 and NE40E-X2, there are no LPUs and SFUs, and NPUs implement the same functions
of LPUs and SFUs to exchange and forward packets.
Related Versions
The following table lists the product versions related to this document.
Product Name
HUAWEI NetEngine80E/40E
Router
Intended Audience
This document is intended for:
l Commissioning Engineer
l Data Configuration Engineer
l Network Monitoring Engineer
l System Maintenance Engineer
Version
V600R003C00
Symbol Conventions
The symbols that may be found in this document are defined as follows.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
ii
Page 4
DANGER
WARNING
CAUTION
TIP
NOTE
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations About This Document
Symbol Description
Alerts you to a high risk hazard that could, if not avoided,
result in serious injury or death.
Alerts you to a medium or low risk hazard that could, if
not avoided, result in moderate or minor injury.
Alerts you to a potentially hazardous situation that could,
if not avoided, result in equipment damage, data loss,
performance deterioration, or unanticipated results.
Provides a tip that may help you solve a problem or save
time.
Provides additional information to emphasize or
supplement important points in the main text.
Command Conventions
The command conventions that may be found in this document are defined as follows.
Convention
Boldface The keywords of a command line are in boldface.
Italic Command arguments are in italics.
[ ] Items (keywords or arguments) in brackets [ ] are optional.
{ x | y | ... } Optional items are grouped in braces and separated by
[ x | y | ... ] Optional items are grouped in brackets and separated by
{ x | y | ... }
[ x | y | ... ]
&<1-n> The parameter before the & sign can be repeated 1 to n times.
*
*
Description
vertical bars. One item is selected.
vertical bars. One item is selected or no item is selected.
Optional items are grouped in braces and separated by
vertical bars. A minimum of one item or a maximum of all
items can be selected.
Optional items are grouped in brackets and separated by
vertical bars. Several items or no item can be selected.
# A line starting with the # sign is comments.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
iii
Page 5
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations About This Document
Change History
Changes between document issues are cumulative. The latest document issue contains all the
changes made in earlier issues.
Changes in Issue 02 (2011-09-10)
The second commercial release.
l Device Maintenance
10.8 Configuring a Working Mode for an LPUF-40 or LPUF-20/21 is added to describe
the configuration of service mode for an LPUF-20/21 or LPUF-40.
Changes in Issue 01 (2011-06-30)
Initial commercial release.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
iv
Page 6
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
Contents
About This Document.....................................................................................................................ii
1 Logging In to the System for the First Time............................................................................1
1.1 Introduction to Log In to the Device for the First Time.....................................................................................2
1.2 Logging In to the Device Through the Console Port..........................................................................................2
1.2.1 Establishing the Configuration Task.........................................................................................................2
1.2.2 Establishing the Physical Connection........................................................................................................3
1.2.3 Logging in to the router.............................................................................................................................3
1.3 Logging In to the router That Supports the Plug-and-Play Function.................................................................5
2 CLI Overview.................................................................................................................................7
2.1 CLI Introduction.................................................................................................................................................8
2.1.1 Command Line Interface...........................................................................................................................8
2.1.2 Command Levels.......................................................................................................................................8
2.1.3 Command Line Views.............................................................................................................................11
2.2 Online Help.......................................................................................................................................................12
2.2.1 Full Help..................................................................................................................................................12
2.2.2 Partial Help..............................................................................................................................................13
2.2.3 Error Messages of the Command Line Interface.....................................................................................13
2.3 CLI Features.....................................................................................................................................................14
2.3.1 Editing.....................................................................................................................................................14
2.3.2 Displaying................................................................................................................................................14
2.3.3 Regular Expressions................................................................................................................................15
2.3.4 Previously-Used Commands...................................................................................................................18
2.3.5 Batch Command Execution.....................................................................................................................19
2.4 Shortcut Keys...................................................................................................................................................20
2.4.1 Classifying Shortcut Keys.......................................................................................................................20
2.4.2 Defining Shortcut Keys...........................................................................................................................22
2.4.3 Use of Shortcut Keys...............................................................................................................................22
2.5 Configuration Examples...................................................................................................................................23
2.5.1 Example for Running Commands in Batches..........................................................................................23
2.5.2 Example for Using Tab............................................................................................................................24
2.5.3 Example for Using Shortcut Keys...........................................................................................................25
2.5.4 Example for Copying Commands Using Shortcut Keys.........................................................................25
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
v
Page 7
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
3 Basic Configuration.....................................................................................................................27
3.1 Configuring the Basic System Environment....................................................................................................28
3.1.1 Establishing the Configuration Task.......................................................................................................28
3.1.2 Switching the Language Mode................................................................................................................28
3.1.3 Configuring the Equipment Name...........................................................................................................29
3.1.4 Setting the System Clock.........................................................................................................................29
3.1.5 Configuring a Header..............................................................................................................................30
3.1.6 Configuring Command Levels................................................................................................................31
3.1.7 Configuring the Undo Command to Match in the Previous View Automatically..................................32
3.2 Displaying System Status Messages.................................................................................................................33
3.2.1 Displaying System Configuration...........................................................................................................33
3.2.2 Displaying System Status........................................................................................................................34
3.2.3 Collecting System Diagnostic Information.............................................................................................34
4 Configuring User Interface........................................................................................................35
4.1 User Interface Overview...................................................................................................................................36
4.2 Configuring the Console User Interface...........................................................................................................38
4.2.1 Establishing the Configuration Task.......................................................................................................38
4.2.2 Setting Physical Attributes of Console User Interface............................................................................38
4.2.3 Setting Terminal Attributes of Console User Interface...........................................................................40
4.2.4 Configuring User Priority of Console User Interface..............................................................................41
4.2.5 Configuring the User Authentication Mode of the Console User Interface............................................41
4.2.6 Checking the Configuration.....................................................................................................................43
4.3 Configuring the AUX User Interface...............................................................................................................44
4.3.1 Establishing the Configuration Task.......................................................................................................44
4.3.2 Setting Physical Attributes of AUX User Interface.................................................................................44
4.3.3 Setting Terminal Attributes of AUX User Interface................................................................................46
4.3.4 Setting User Priority of AUX User Interface..........................................................................................47
4.3.5 Setting Modem Attributes of AUX User Interface..................................................................................47
4.3.6 (Optional) Configuring Auto-Execute Commands of AUX User Interface............................................48
4.3.7 Setting User Authentication Mode of AUX User Interface.....................................................................49
4.3.8 Checking the Configuration.....................................................................................................................50
4.4 Configuring VTY User Interface......................................................................................................................51
4.4.1 Establishing the Configuration Task.......................................................................................................51
4.4.2 Configuring Maximum VTY User Interfaces.........................................................................................52
4.4.3 (Optional)Setting Limit on Incoming and Outgoing Calls of VTY User Interfaces...............................53
4.4.4 Setting Terminal Attributes of the VTY User Interface..........................................................................53
4.4.5 Setting User Priority of VTY User Interface...........................................................................................54
4.4.6 Setting User Authentication Mode of the VTY User Interface...............................................................55
4.4.7 (Optional) Configuring NMS Users to Log In Through VTY User Interfaces.......................................56
4.4.8 Checking the Configuration.....................................................................................................................58
4.5 Configuration Examples...................................................................................................................................59
4.5.1 Example for Configuring Console User Interface...................................................................................59
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
vi
Page 8
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
4.5.2 Example for Configuring AUX User Interface.......................................................................................61
4.5.3 Example for Configuring VTY User Interface........................................................................................63
5 Configuring User Login.............................................................................................................65
5.1 Overview of User Login...................................................................................................................................67
5.2 Logging in to the Devices Through the Console Port......................................................................................67
5.2.1 Establishing the Configuration Task.......................................................................................................68
5.2.2 Configuring Console User Interface........................................................................................................68
5.2.3 Logging in to the router Through a Console Port....................................................................................68
5.2.4 Checking the Configuration.....................................................................................................................69
5.3 Logging in to the Devices Through the AUX Port...........................................................................................70
5.3.1 Establishing the Configuration Task.......................................................................................................70
5.3.2 Configuring AUX User Interface............................................................................................................71
5.3.3 Logging in to the routerThrough an AUX Port.......................................................................................71
5.3.4 Checking the Configuration.....................................................................................................................74
5.4 Logging in to the Devices by Using Telnet......................................................................................................75
5.4.1 Establishing the Configuration Task.......................................................................................................75
5.4.2 Configuring VTY User Interface.............................................................................................................76
5.4.3 (Optional) Configuring Local Telnet Users.............................................................................................77
5.4.4 Enabling the Telnet Service.....................................................................................................................77
5.4.5 (Optional) Configuring Listening Port Number for Telnet Server..........................................................78
5.4.6 Logging in to the router by Using Telnet................................................................................................79
5.4.7 Checking the Configuration.....................................................................................................................80
5.5 Logging in to the Devices by Using STelnet....................................................................................................81
5.5.1 Establishing the Configuration Task.......................................................................................................81
5.5.2 Configuring VTY User Interface.............................................................................................................82
5.5.3 Configuring SSH for the VTY User Interface.........................................................................................82
5.5.4 Configuring an SSH User and Specifying STelnet as One of Service Types.........................................83
5.5.5 Enabling the STelnet Server Function.....................................................................................................86
5.5.6 (Optional) Configuring the STelnet Server Parameters...........................................................................86
5.5.7 Logging in to the router by Using STelnet..............................................................................................88
5.5.8 Checking the Configuration.....................................................................................................................89
5.6 Common Operations After Login.....................................................................................................................90
5.6.1 Establishing the Configuration Task.......................................................................................................90
5.6.2 Switching User Levels.............................................................................................................................90
5.6.3 Locking User Interfaces...........................................................................................................................91
5.6.4 Sending Messages to Other User Interfaces............................................................................................92
5.6.5 Displaying Logged-in Users....................................................................................................................92
5.6.6 Clearing Logged-in Users........................................................................................................................93
5.6.7 Configuring Configuration Locking........................................................................................................93
5.7 Configuration Examples...................................................................................................................................94
5.7.1 Example for Configuring User Login Through a Console Port..............................................................94
5.7.2 Example for Logging In Through the AUX Port....................................................................................97
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
vii
Page 9
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
5.7.3 Example for Configuring User Login by Using Telnet...........................................................................98
5.7.4 Example for Configuring User Login by Using STelnet.......................................................................101
6 Managing File System..............................................................................................................105
6.1 File System Overview....................................................................................................................................106
6.1.1 File System............................................................................................................................................106
6.1.2 Methods of File Management................................................................................................................106
6.2 Performing File Operations by Means of the File System.............................................................................107
6.2.1 Establishing the Configuration Task.....................................................................................................107
6.2.2 Managing Storage Devices....................................................................................................................108
6.2.3 Managing the Directory.........................................................................................................................108
6.2.4 Managing Files......................................................................................................................................109
6.3 Performing File Operations by Means of FTP...............................................................................................111
6.3.1 Establishing the Configuration Task.....................................................................................................112
6.3.2 Configuring a Local FTP User..............................................................................................................112
6.3.3 (Optional) Specifying a Port Number for the FTP Server.....................................................................113
6.3.4 Enabling the FTP Server........................................................................................................................114
6.3.5 (Optional) Configuring the FTP Server Parameters..............................................................................114
6.3.6 (Optional) Configuring an FTP ACL....................................................................................................115
6.3.7 Accessing the System by Using FTP.....................................................................................................116
6.3.8 Performing File Operations by Using FTP Commands.........................................................................117
6.3.9 Checking the Configuration...................................................................................................................119
6.4 Performing File Operations by Means of SFTP.............................................................................................119
6.4.1 Establishing the Configuration Task.....................................................................................................119
6.4.2 Configuring VTY User Interface...........................................................................................................120
6.4.3 Configuring SSH for the VTY User Interface.......................................................................................120
6.4.4 Configuring an SSH User and Specifying SFTP as One of Service Types...........................................121
6.4.5 Enabling the SFTP Service....................................................................................................................124
6.4.6 (Optional) Configuring the STelnet Server Parameters.........................................................................125
6.4.7 Accessing the System by Using SFTP..................................................................................................126
6.4.8 Performing File Operations by Using SFTP..........................................................................................127
6.4.9 Checking the Configuration...................................................................................................................128
6.5 Performing File Operations by Means of Xmodem.......................................................................................129
6.5.1 Establishing the Configuration Task.....................................................................................................130
6.5.2 Getting a File Through Xmodem...........................................................................................................130
6.6 Configuration Examples.................................................................................................................................131
6.6.1 Example for Performing File Operations by Means of the File System...............................................131
6.6.2 Example for Performing File Operations by Means of FTP.................................................................132
6.6.3 Example for Performing File Operations by Means of SFTP...............................................................135
6.6.4 Example for Performing File Operations by Means of Xmodem..........................................................137
7 Configuring System Startup....................................................................................................140
7.1 System Startup Overview...............................................................................................................................141
7.1.1 System Software....................................................................................................................................141
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
viii
Page 10
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
7.1.2 Configuration Files................................................................................................................................141
7.1.3 Configuration Files and Current Configurations...................................................................................141
7.2 Managing Configuration Files........................................................................................................................142
7.2.1 Establishing the Configuration Task.....................................................................................................142
7.2.2 Saving Configuration Files....................................................................................................................143
7.2.3 Clearing a Configuration File................................................................................................................144
7.2.4 Comparing Configuration Files.............................................................................................................145
7.2.5 Checking the Configuration...................................................................................................................146
7.3 Specifying a File for System Startup..............................................................................................................147
7.3.1 Establishing the Configuration Task.....................................................................................................147
7.3.2 Configuring System Software for a router to Load for the Next Startup..............................................147
7.3.3 Configuring the Configuration File for Router to Load for the Next Startup.......................................148
7.3.4 Checking the Configuration...................................................................................................................148
7.4 Configuration Examples.................................................................................................................................149
7.4.1 Example for Configuring System Startup.............................................................................................149
8 Accessing Another Device.......................................................................................................152
8.1 Accessing Another Device.............................................................................................................................153
8.1.1 Telnet Method........................................................................................................................................153
8.1.2 FTP Method...........................................................................................................................................155
8.1.3 TFTP Method........................................................................................................................................155
8.1.4 SSH Method..........................................................................................................................................156
8.2 Logging in to Other Devices by Using Telnet................................................................................................157
8.2.1 Establishing the Configuration Task.....................................................................................................157
8.2.2 (Optional) Configuring a Source IP Address for an Telnet Client........................................................158
8.2.3 Logging in to Another Device by Using Telnet....................................................................................158
8.2.4 Checking the Configuration...................................................................................................................159
8.3 Connecting to Another Device by Using the Telnet Redirection Function....................................................160
8.3.1 Establishing the Configuration Task.....................................................................................................160
8.3.2 Enabling the Telnet Redirection Function.............................................................................................161
8.3.3 Connecting Another Device by Using the Telnet Redirection Function...............................................162
8.3.4 Checking the Configuration...................................................................................................................162
8.4 Logging in to Another Device by Using STelnet...........................................................................................163
8.4.1 Establishing the Configuration Task.....................................................................................................163
8.4.2 Configuring the First Successful Login to Another Device (Enabling the First-Time Authentication on
the SSH Client)...............................................................................................................................................163
8.4.3 Configuring the First Successful Login to Another Device (Allocating an RSA Public Key to the SSH
Server)............................................................................................................................................................164
8.4.4 Logging in to Another Device by Using STelnet..................................................................................166
8.4.5 Checking the configuration...................................................................................................................166
8.5 Accessing Files on Another Device by Using TFTP......................................................................................167
8.5.1 Establishing the Configuration Task.....................................................................................................167
8.5.2 (Optional) Configuring a Source IP Address for a TFTP Client...........................................................168
8.5.3 (Optional) Configuring TFTP Access Authority...................................................................................168
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
ix
Page 11
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
8.5.4 Downloading Files by Using TFTP.......................................................................................................169
8.5.5 Uploading Files by Using TFTP............................................................................................................169
8.5.6 Checking the Configuration...................................................................................................................170
8.6 Accessing Files on Another Device by Using FTP........................................................................................170
8.6.1 Establishing the Configuration Task.....................................................................................................171
8.6.2 (Optional) Configuring Source IP Address and Interface of the FTP Client........................................171
8.6.3 Connecting to Other Devices by Using FTP Commands......................................................................172
8.6.4 Operating Files by Using FTP Commands............................................................................................173
8.6.5 Changing Login Users...........................................................................................................................175
8.6.6 Disconnecting from the FTP Server......................................................................................................176
8.6.7 Checking the Configuration...................................................................................................................176
8.7 Accessing Files on Another Device by Using SFTP......................................................................................177
8.7.1 Establishing the Configuration Task.....................................................................................................177
8.7.2 (Optional) Configuring a Source IP Address for an SFTP Client.........................................................178
8.7.3 Configuring the First Successful Login to Another Device (Enabling the First-Time Authentication on
the SSH Client)...............................................................................................................................................178
8.7.4 Configuring the First Successful Login to Another Device (Allocating an RSA Public Key to the SSH
Server)............................................................................................................................................................179
8.7.5 Connecting to Other Devices by Using SFTP.......................................................................................180
8.7.6 Operating Files by Using SFTP Commands..........................................................................................181
8.7.7 Checking the Configuration...................................................................................................................183
8.8 Configuration Examples.................................................................................................................................183
8.8.1 Example for Logging in to Another Device by Using Telnet...............................................................183
8.8.2 Example for Logging in to Another Device by Using the Telnet Redirection Function.......................186
8.8.3 Example for Logging in to Another Device by Using Telnet on a VPN...............................................187
8.8.4 Example for Configuring the Device as the STelnet Client to Connect to the SSH Server..................189
8.8.5 Example for Accessing Files on Another Device by Using TFTP........................................................195
8.8.6 Example for Configuring the Access of the TFTP Server on the Public Network When the Management
VPN Instance Is Used.....................................................................................................................................197
8.8.7 Example for Accessing Files on Another Device by Using FTP..........................................................199
8.8.8 Example for Configuring the Access of the FTP Server on the Public Network When the Management
VPN Instance Is Used.....................................................................................................................................201
8.8.9 Example for Accessing Files on Another Device by Using SFTP........................................................202
8.8.10 Example for Configuring the Access of the SFTP Server on the Public Network When the Management
VPN Instance Is Used.....................................................................................................................................208
8.8.11 Example for Accessing the SSH Server Through Other Port Numbers..............................................213
8.8.12 Example for an SSH Client in the Public Network to Access an SSH Server in the Private Network
........................................................................................................................................................................219
9 Clock Synchronization Configuration..................................................................................229
9.1 Introduction of Clock Synchronization Configuration...................................................................................230
9.1.1 Overview of Clock Synchronization Configuration..............................................................................230
9.1.2 Clock Synchronization Supported by the NE80E/40E..........................................................................230
9.2 Setting Basic Configurations for Clock Synchronization...............................................................................230
9.2.1 Establishing the Configuration Task.....................................................................................................231
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
x
Page 12
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
9.2.2 Setting Basic Configurations for Clock Synchronization......................................................................231
9.2.3 Checking the Configuration...................................................................................................................232
9.3 Configuring an External BITS Clock Source.................................................................................................232
9.3.1 Establishing the Configuration Task.....................................................................................................233
9.3.2 Configuring the Lower Threshold of the Clock Signals Output by the BITS Clock............................233
9.3.3 Configuring an External Clock Source and Its Signal Type on the router............................................233
9.3.4 Checking the Configuration...................................................................................................................234
9.4 Configuring a Clock Reference Source Manually or Forcibly.......................................................................234
9.4.1 Establishing the Configuration Task.....................................................................................................234
9.4.2 Configuring a Clock Reference Source.................................................................................................235
9.4.3 Checking the Configuration...................................................................................................................236
9.5 Configuring Clock Protection Switching Based on SSM Levels...................................................................237
9.5.1 Establishing the Configuration Task.....................................................................................................237
9.5.2 Configuring the Router to Automatically Select Clock Sources...........................................................237
9.5.3 Enabling SSM........................................................................................................................................238
9.5.4 Configuring the SSM Level of the Clock Reference Source.................................................................238
9.5.5 Setting a Timeslot of the 2.048 Mbit/s BITS Clock Signal to Carry SSMs..........................................239
9.5.6 Setting the Modes of Extracting SSM Levels.......................................................................................239
9.5.7 Checking the Configuration...................................................................................................................240
9.6 Configuring Clock Protection Switching Based on Priorities........................................................................241
9.6.1 Establishing the Configuration Task.....................................................................................................241
9.6.2 Configuring the Router to Automatically Select Clock Sources...........................................................241
9.6.3 Disabling SSM.......................................................................................................................................242
9.6.4 Setting Priorities of Clock Reference Sources......................................................................................242
9.6.5 Checking the Configuration...................................................................................................................243
9.7 Configuring Ethernet Clock Synchronization................................................................................................243
9.7.1 Establishing the Configuration Task.....................................................................................................243
9.7.2 Enabling Ethernet Clock Synchronization............................................................................................244
9.7.3 Configuring Ethernet Clock Source......................................................................................................245
9.7.4 Checking the Configuration...................................................................................................................245
9.8 Configuration Examples of Clock Synchronization.......................................................................................246
9.8.1 Example for Configuring Protection Switchover of Clock Sources......................................................246
10 Device Maintenance................................................................................................................254
10.1 Introduction of Device Maintenance............................................................................................................256
10.1.1 Overview of Device Maintenance.......................................................................................................256
10.1.2 Maintenance Features Supported by the NE80E/40E.........................................................................256
10.2 Powering off the MPU..................................................................................................................................256
10.2.1 Establishing the Configuration Task...................................................................................................256
10.2.2 Powering off the Slave MPU...............................................................................................................257
10.2.3 Checking the Configuration.................................................................................................................258
10.3 Powering off the SFU...................................................................................................................................258
10.3.1 Establishing the Configuration Task...................................................................................................259
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
xi
Page 13
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
10.3.2 Powering off the SFU..........................................................................................................................259
10.3.3 Checking the Configuration.................................................................................................................260
10.4 Powering off the NPU..................................................................................................................................260
10.4.1 Establishing the Configuration Task...................................................................................................261
10.4.2 Powering off the NPU.........................................................................................................................261
10.4.3 Checking the Configuration.................................................................................................................262
10.5 Powering off the LPU...................................................................................................................................262
10.5.1 Establishing the Configuration Task...................................................................................................262
10.5.2 Powering off the LPU..........................................................................................................................263
10.5.3 Checking the Configuration.................................................................................................................263
10.6 Restoring the Bandwidth of 10GE LAN/WAN Interfaces on an NPU to 10 Gbit/s....................................264
10.6.1 Establishing the Configuration Task...................................................................................................264
10.6.2 Restoring the bandwidth of 10GE LAN/WAN interfaces on an NPU to 10 Gbit/s............................265
10.6.3 Checking the Configuration.................................................................................................................265
10.7 Switching Between the Operation Modes of the LPUF-10..........................................................................266
10.7.1 Establishing the Configuration Task...................................................................................................266
10.7.2 Switching Between the Operation Modes of the LPUF-10.................................................................267
10.7.3 Checking the Configuration.................................................................................................................267
10.8 Configuring a Working Mode for an LPUF-40 or LPUF-20/21..................................................................268
10.8.1 Establishing the Configuration Task...................................................................................................268
10.8.2 Configuring a Service Mode for an LPUF-20/21 or LPUF-40...........................................................269
10.8.3 Checking the Configuration.................................................................................................................270
10.9 Configuring the CMU...................................................................................................................................271
10.9.1 Establishing the Configuration Task...................................................................................................271
10.9.2 Configuring Monitor Items for a CMU...............................................................................................271
10.10 Configuring a Cleaning Cycle for the Air Filter.........................................................................................272
10.10.1 Establishing the Configuration Task.................................................................................................272
10.10.2 Configuring a Cleaning Cycle for the Air Filter................................................................................272
10.10.3 Remonitoring the Cleaning Cycle of the Air Filter...........................................................................273
10.10.4 Checking the Configuration...............................................................................................................273
10.11 Monitoring the Device Status.....................................................................................................................274
10.11.1 Displaying the System Version Information.....................................................................................274
10.11.2 Displaying Basic Information About the Router...............................................................................274
10.11.3 Displaying the Electronic Label........................................................................................................275
10.11.4 Displaying the Soft Boot Mode.........................................................................................................275
10.11.5 Displaying the Threshold of the Memory Usage...............................................................................276
10.11.6 Displaying the Threshold of CPU Usage..........................................................................................276
10.11.7 Displaying Alarm Information..........................................................................................................276
10.11.8 Displaying the Board Temperature....................................................................................................277
10.11.9 Displaying the Board Voltage...........................................................................................................277
10.11.10 Displaying the Power Supply Status...............................................................................................278
10.11.11 Displaying Current Information About Boards...............................................................................278
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
xii
Page 14
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
10.11.12 Displaying Entironment Information About the Device.................................................................279
10.11.13 Displaying the Fan Status................................................................................................................279
10.11.14 Displaying the Sequence Number of the MPU...............................................................................279
10.11.15 Displaying the Next Start Mode of the Board.................................................................................280
10.11.16 Displaying the Number of the Registered SFUs By Default...........................................................280
10.12 Board Maintence ........................................................................................................................................281
10.12.1 Resetting a Board...............................................................................................................................281
10.12.2 Clearing the Maximum CPU Usage..................................................................................................281
10.13 Configuring NAP-based Remote Deployment...........................................................................................282
10.13.1 Establishing the Configuration Task.................................................................................................282
10.13.2 Configuring and Starting the NAP Master Interface.........................................................................283
10.13.3 Remote Login....................................................................................................................................285
10.13.4 Disabling NAP on the Slave Device..................................................................................................285
10.13.5 Checking the Configuration...............................................................................................................286
10.14 Configuration Examples of the Device Maintenance.................................................................................287
10.14.1 Example for Powering off the MPU..................................................................................................287
10.14.2 Example for Powering off the SFU...................................................................................................289
10.14.3 Example for Powering off the LPU...................................................................................................290
10.14.4 Example for Configuring the Operation Mode of the LPUF-10.......................................................291
10.14.5 Example for Configuring NAP-based Remote Deployment in Automatic Mode.............................292
10.14.6 Example for Configuring NAP-based Remote Deployment in Static Mode.....................................293
11 Device Upgrading....................................................................................................................296
11.1 Overview of Device Upgrade.......................................................................................................................297
11.2 Upgrade Modes Supported by the NE80E/40E............................................................................................297
12 Patch Management..................................................................................................................299
12.1 Introduction of Patch Management..............................................................................................................300
12.1.1 Overview of Patch Management.........................................................................................................300
12.1.2 Patches Supported by the NE80E/40E................................................................................................301
12.2 Checking the Running of Patch in the System.............................................................................................302
12.2.1 Establishing the Configuration Task...................................................................................................302
12.2.2 Checking the Running of Patch in the System....................................................................................303
12.2.3 (Optional) Deleting a Patch.................................................................................................................303
12.3 Loading a Patch............................................................................................................................................304
12.3.1 Establishing the Configuration Task...................................................................................................304
12.3.2 Loading a Patch...................................................................................................................................304
12.3.3 Checking the Configuration.................................................................................................................305
12.4 Installing a Patch..........................................................................................................................................306
12.4.1 Establishing the Configuration Task...................................................................................................306
12.4.2 Loading a Patch...................................................................................................................................307
12.4.3 Activating a Patch................................................................................................................................307
12.4.4 Running a Patch...................................................................................................................................308
12.4.5 (Optional) Synchronizing Patches.......................................................................................................308
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
xiii
Page 15
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations Contents
12.4.6 Checking the Configuration.................................................................................................................309
12.5 (Optional) Unactivating the activating of Patch...........................................................................................313
12.5.1 Establishing the Configuration Task...................................................................................................313
12.5.2 Deactivating a Patch............................................................................................................................313
12.5.3 Checking the Configuration.................................................................................................................313
12.6 Configuration Examples of the Patch Management.....................................................................................314
12.6.1 Example for Installing a Patch.............................................................................................................314
A Glossary......................................................................................................................................317
B Acronyms and Abbreviations.................................................................................................323
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
xiv
Page 16
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
1 Logging In to the System for the First Time
About This Chapter
You can log in to a new router through the console port to configure the router.
1.1 Introduction to Log In to the Device for the First Time
A user can log in to the router that is powered on for the first time through the console port or
by the plug-and-play function to configure the router.
1.2 Logging In to the Device Through the Console Port
This section describes how to connect a terminal to a router through the console port to establish
the configuration environment.
1.3 Logging In to the router That Supports the Plug-and-Play Function
The plug-and-play function enables the router to automatically access the network and obtains
an IP address after the router is powered on. This allows engineers to remotely log in to the
router to perform basic configurations.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
1
Page 17
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
1.1 Introduction to Log In to the Device for the First Time
A user can log in to the router that is powered on for the first time through the console port or
by the plug-and-play function to configure the router.
Log in to the router through the console port
The console port is a linear port on the main control board.
Each main control board provides one console port that conforms to the EIA/TIA-232 standard
and whose type is DCE. The serial interface of a terminal can be directly connected to the console
port on the router. Users can then configure the router on the terminal.
NOTE
When a device is powered on for the first time, you must log in to the device through the console port. It
is a prerequisite for other login modes. For example, the IP address for Telnet login must be configured by
logging in to the device through the console port.
Log in to the router by the plug-and-play function
NOTE
The plug-and-play function only can be configured on the X1 , X2 and X3 models of the NE80E/40E.
During site deployment, the routers reside far away from the equipment room. Sending software
commissioning engineers to deploy the network at the site is quite costly. After the plug-andplay function is enabled, however, the router automatically obtains an IP address. Software
commissioning engineers are able to remotely deliver configurations to the router through the
NMS after installation personnel finishes hardware installation. This greatly simplifies
installation and reduces costs with minimized site visits.
The plug-and-play function is controlled by a PAF file and users do not need to configure it
manually. This function is automatically disabled after the router correctly obtains an IP address.
1.2 Logging In to the Device Through the Console Port
This section describes how to connect a terminal to a router through the console port to establish
the configuration environment.
1.2.1 Establishing the Configuration Task
Before logging in to the router through the console port, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This will help
you complete the configuration task quickly and accurately.
Applicable Environment
When the router is powered on for the first time, you need to use the console port to log in to
the router to configure and manage the router.
Pre-configuration Tasks
Before logging in to the router through the console port, complete the following tasks:
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
2
Page 18
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
l Installing terminal emulation program on the PC (such as Windows XP HyperTerminal)
l Preparing the RS-232 cable
Data Preparation
To log in to the router through the console port, you need the following data.
No. Data
1 Terminal communication parameters
l Baud rate
l Data bit
l Parity
l Stop bit
l Flow-control mode
NOTE
When the router is logged in for the first time, the system automatically uses default parameter values.
1.2.2 Establishing the Physical Connection
The console port on the router must be connected to the COM port on a terminal by using a
console cable.
Procedure
Step 1 Power on all devices to perform a self-check.
Step 2 Connect the COM port on the PC and the console port on the router by a cable.
----End
1.2.3 Logging in to the router
You can log in to the router through the console port to configure and manage the router that is
powered on for the first time.
Context
You need to configure terminal attributes for the PC according to the attributes configured for
the console port, including the transmission rate, data bit, parity bit, stop bit, and flow control
mode. As the router is logged in for the first time, every terminal attribute uses the default value
of the router.
Procedure
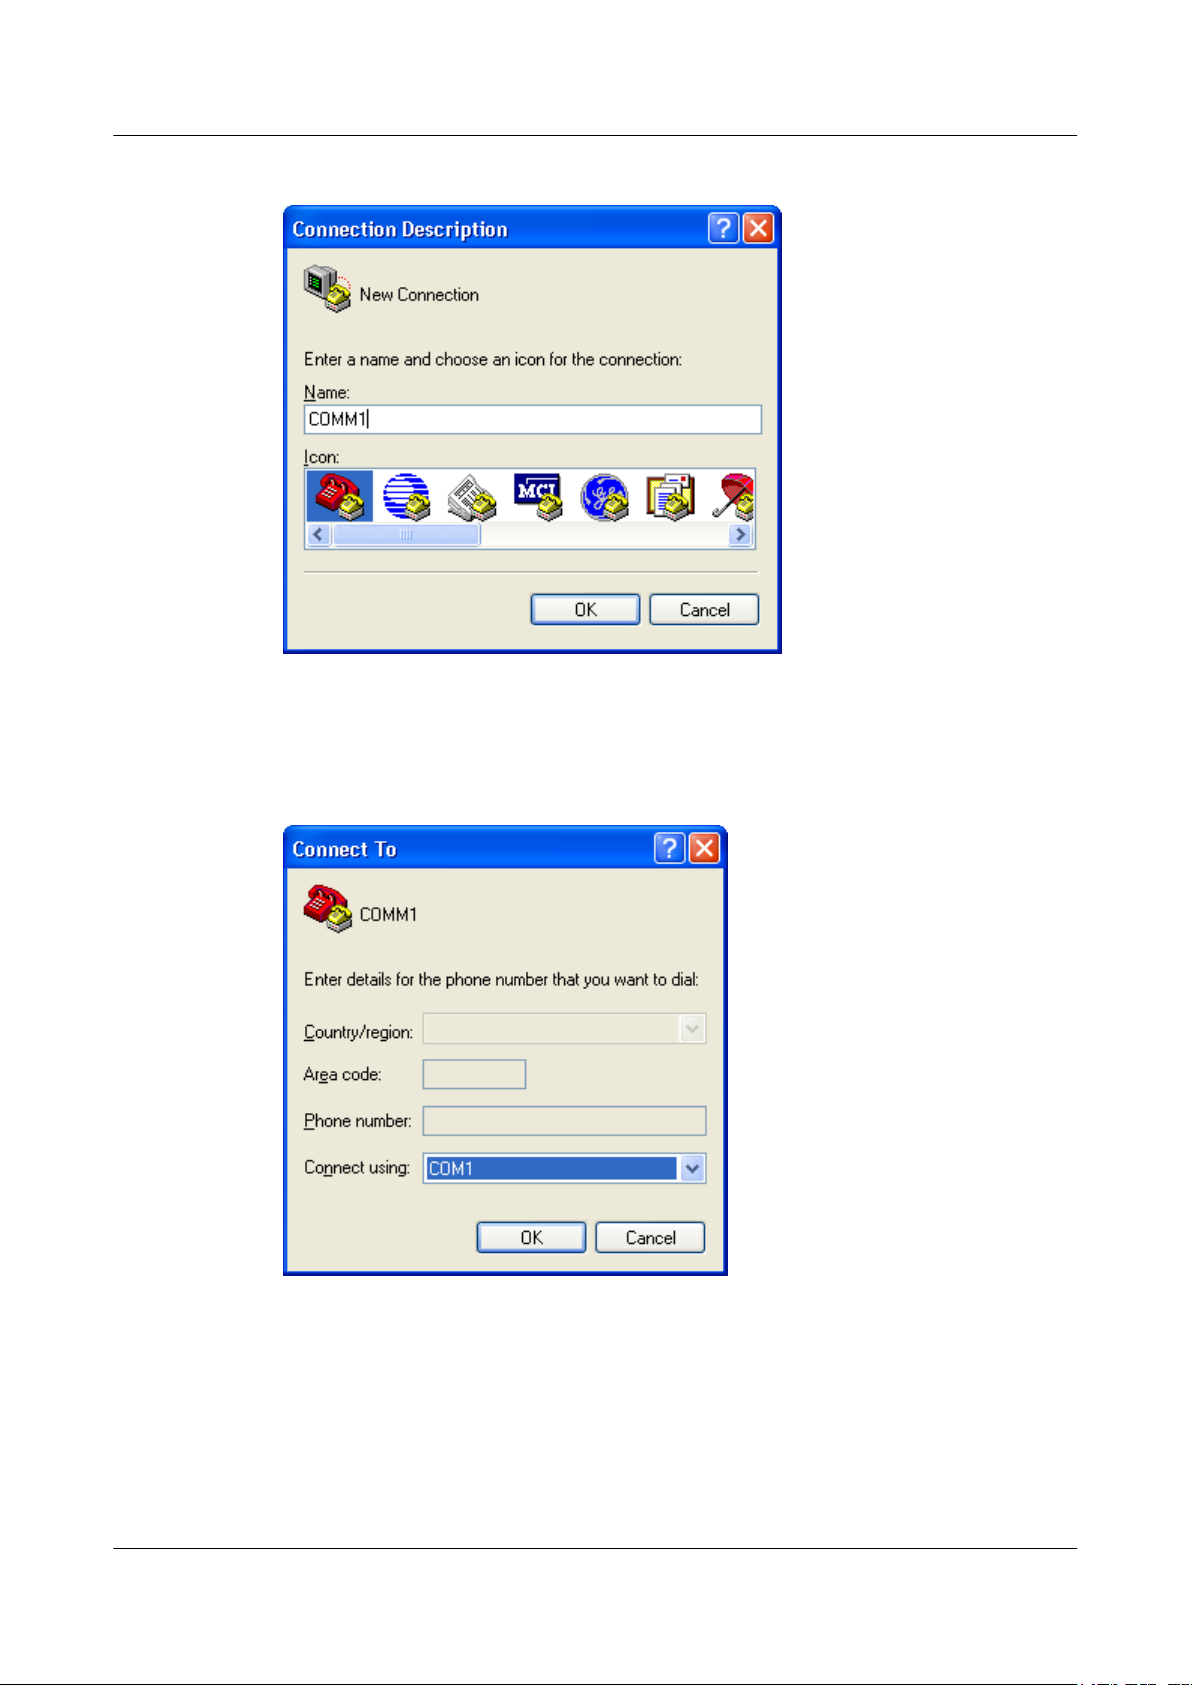
Step 1 Start a terminal emulator on the PC, and create a new connection, as shown in Figure 1-1.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
3
Page 19
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
Figure 1-1 Connection creation
Step 2 Set interface,as shown in Figure 1-2.
Figure 1-2 Interface setting
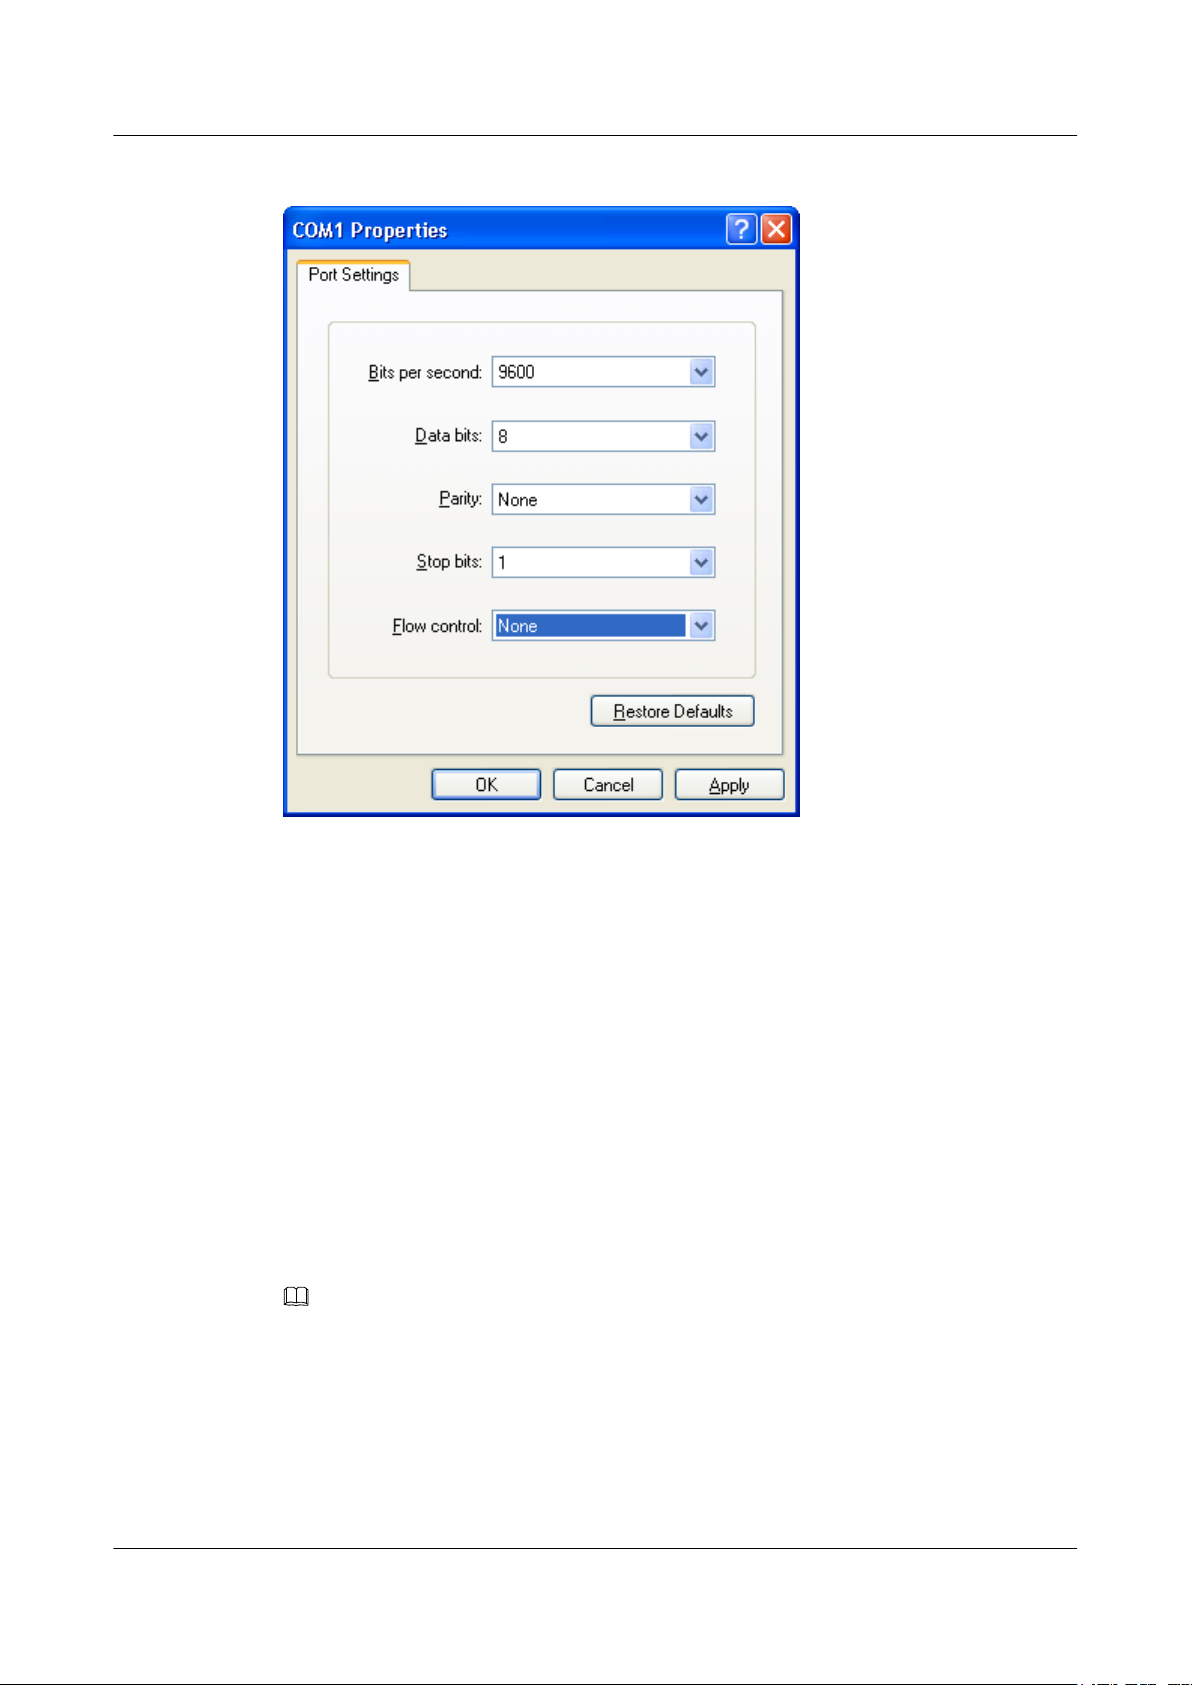
Step 3 Set communication parameter, same as the default of router,as shown in Figure 1-3.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
4
Page 20
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
Figure 1-3 Communication parameter setting
Step 4 Press Enter. A command line prompt such as <HUAWEI> appears, and the user view is
displayed for you to configure the router.
----End
1.3 Logging In to the router That Supports the Plug-and-Play Function
The plug-and-play function enables the router to automatically access the network and obtains
an IP address after the router is powered on. This allows engineers to remotely log in to the
router to perform basic configurations.
Context
NOTE
The plug-and-play function only can be configured on the X1 , X2 and X3 models of the NE80E/40E.
During site deployment, the routers reside far away from the equipment room. Sending software
commissioning engineers to deploy the network at the site is quite costly. After the plug-andplay function is enabled, however, the router automatically obtains an IP address. Software
commissioning engineers are able to remotely deliver configurations to the router through the
NMS after installation personnel finishes hardware installation. This greatly simplifies
installation and reduces costs with minimized site visits. The plug-and-play function is controlled
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
5
Page 21
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 1 Logging In to the System for the First Time
by a PAF file and users do not need to configure it manually. This function is automatically
disabled after the router correctly obtains an IP address. The process of logging in to the
router supporting the plug-and-play function is as follows:
Procedure
Step 1 After planning the network, network planning engineers provide a planning list for software
commissioning engineers.
Step 2 Based on the planning list, software commissioning engineers configure the mappings between
the router locations and IP addresses on the DHCP server, compile configuration scripts, and
configure the mappings between the router locations and scripts.
Step 3 Hardware installation personnel installs the router and power them on at the site.
Step 4 The router sends a DHCPREQUEST message to the DHCP server, and then the interface
connecting to the DHCP server obtains an IP address.
Step 5 The NMS delivers configurations to the router.
----End
Follow-up Procedure
If there is no DHCP server on the network or the router cannot obtain an IP address for some
reason, the router displays the following information:
PNP State!!!PLEASE UNDO PNP enable for manual Setup!
You can undo PNP in system view with "undo pnp enable"
At this time, do as follows to disable the plug-and-play function:
1. Run the system-view command to enter the system view.
2. Run the undo pnp enable command to disable the plug-and-play function.
3. Run the undo pnp default route command to delete the default route generated by the
plug-and-play function.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
6
Page 22
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2 CLI Overview
About This Chapter
The command line interface (CLI) is used to configure and maintain devices.
2.1 CLI Introduction
After you log in to the router, a prompt is displayed, indicating that you enter the command line
interface (CLI). The CLI is used by users to interact with the router.
2.2 Online Help
When inputting command lines or configuring services, you can use the online help function to
obtain real-time help.
2.3 CLI Features
The CLI provides the following features to help users flexibly use it.
2.4 Shortcut Keys
Using the system or user-defined shortcut keys makes it easier to enter commands.
2.5 Configuration Examples
This section provides several examples for using command lines.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
7
Page 23
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2.1 CLI Introduction
After you log in to the router, a prompt is displayed, indicating that you enter the command line
interface (CLI). The CLI is used by users to interact with the router.
2.1.1 Command Line Interface
You can configure and manage the router by using the CLI commands.
The characteristics of CLI are as follows:
l Local or remote configuration through the AUX port.
l Local configuration through console port.
l Local or remote configuration through Telnet or Secure Shell (SSH).
l Remote configuration by logging in to an asynchronous serial interface on the router
through Modem dialup.
l The telnet command for directly logging in to and managing other routers.
l FTP service for file uploading and downloading.
l A user interface view for specific configuration management.
l Hierarchical command protection for users of different levels, that is, running the
commands of the corresponding levels.
l Three authentication modes are supported, namely, none-authentication, password
authentication, and Authentication, Authorization, and Accounting (AAA) authentication.
Password and AAA authentication prohibit unauthorized users from logging in to the
router, guaranteeing system security.
l Entering "?" for online help at any time.
l A command line interpreter provides intelligent command resolution methods such as key
word fuzzy match and context conjunction. These methods make it easy for users to enter
their commands.
l Network testing commands such as tracert and ping for rapidly diagnosing a network.
l Abundant debugging information to help in diagnosing the network.
l Running a command used previously on the device, like DosKey.
NOTE
l The system supports the command with up to 512 characters. The command can be incomplete. This
means that you can input initial characters (one or some) of the command to represent the whole
command. The incomplete command, however, must be unqiue in the system. For example, to use the
display current-configuration command, just input d cu, di cu, or dis cu. d c or dis c, however, cannot
be input, becuse they are not unique to represent the display current-configuration command.
l The system saves the incomplete command to the configuration files in the complete form; therefore,
the command may have more than 512 characters. When the system is restarted, however, the
incomplete command cannot be restored. Therefore, pay attention to the length of the incomplete
command.
2.1.2 Command Levels
The system manages commands in hierarchy for security. The administrator can set user levels
corresponding to command levels to implement user-specific access control.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
8
Page 24
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
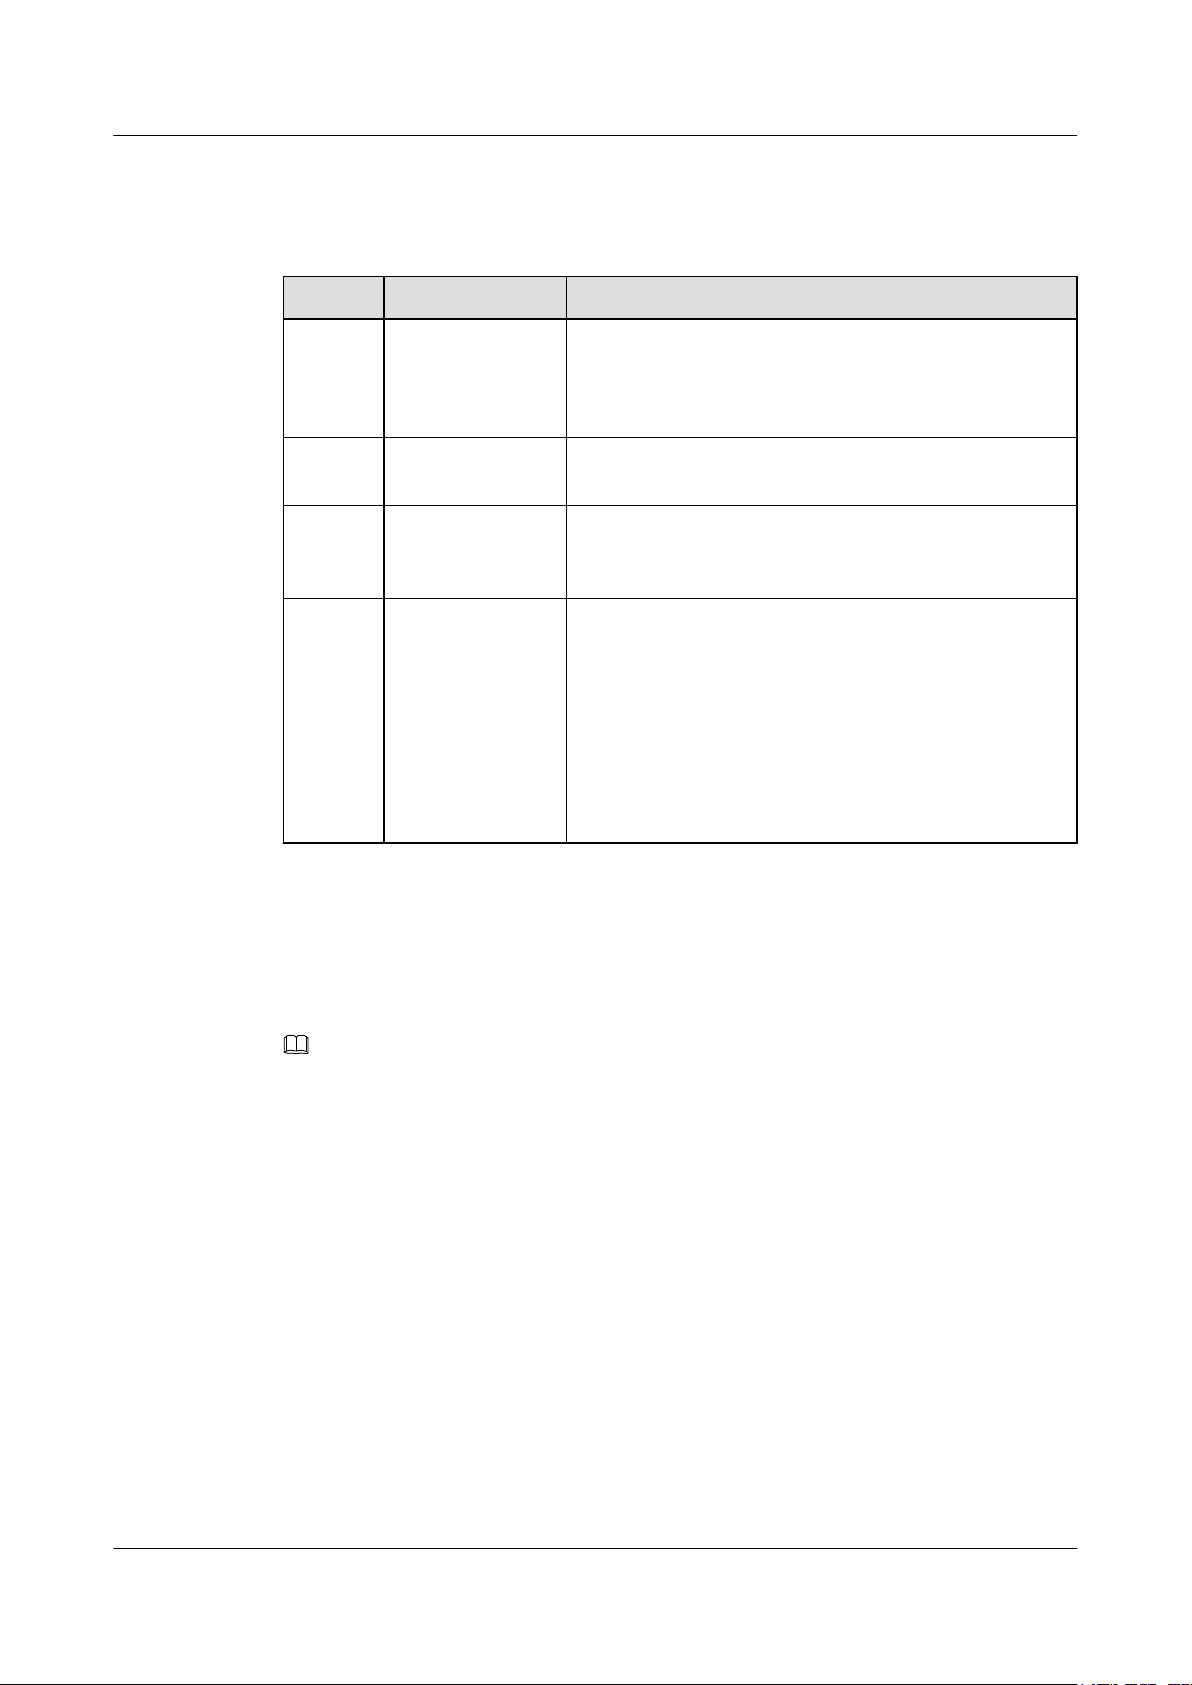
The default command levels are as follows:
Table 2-1 Command line levels
Level Name Description
0 Visit level Commands of this level include commands of network
diagnosis tool (such as ping and tracert) and commands that
start from the local device and visit external device (such
as Telnet client side).
1 Monitoring level Commands of this level, including the display commands,
are used for system maintenance and fault diagnosis.
2 Configuration
level
Commands of this level are service configuration
commands that provide direct network service to the user,
including routing and network layer commands.
3 Management level Commands of this level are commands that influence the
basic operation of the system and provide support to the
service. They include file system commands, FTP
commands, TFTP commands, XModem downloading
commands, configuration file switching commands, power
supply control commands, backup board control
commands, user management commands, level setting
commands, system internal parameter setting commands,
and debugging commands that are used for fault diagnosis.
To implement efficient management, you can increase the command levels to 0-15. For the
increase in the command levels, refer to Chapter 4 "Basic Configuration" Configuring
Command Levels in the HUAWEI NetEngine80E/40E Configuration Guide - Basic
Configurations.
NOTE
l The default command level may be higher than the command level defined according to the command
rules in application.
l The level of the command that a user can run is determined by the level of this user.
l Login users have the same 16 levels as the command levels. The login users can use only the command
of the levels that are equal to or lower than their own levels. The user privilege level level command
sets the user level.
Searching Commands Based on Command Levels
You can search for all commands of a specific level simultaneously. The procedure is as follows:
1. Open the command reference (.chm.) file.
2. Click the "Search" tab. The search window will be displayed as shown in Figure 2-1.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
9
Page 25
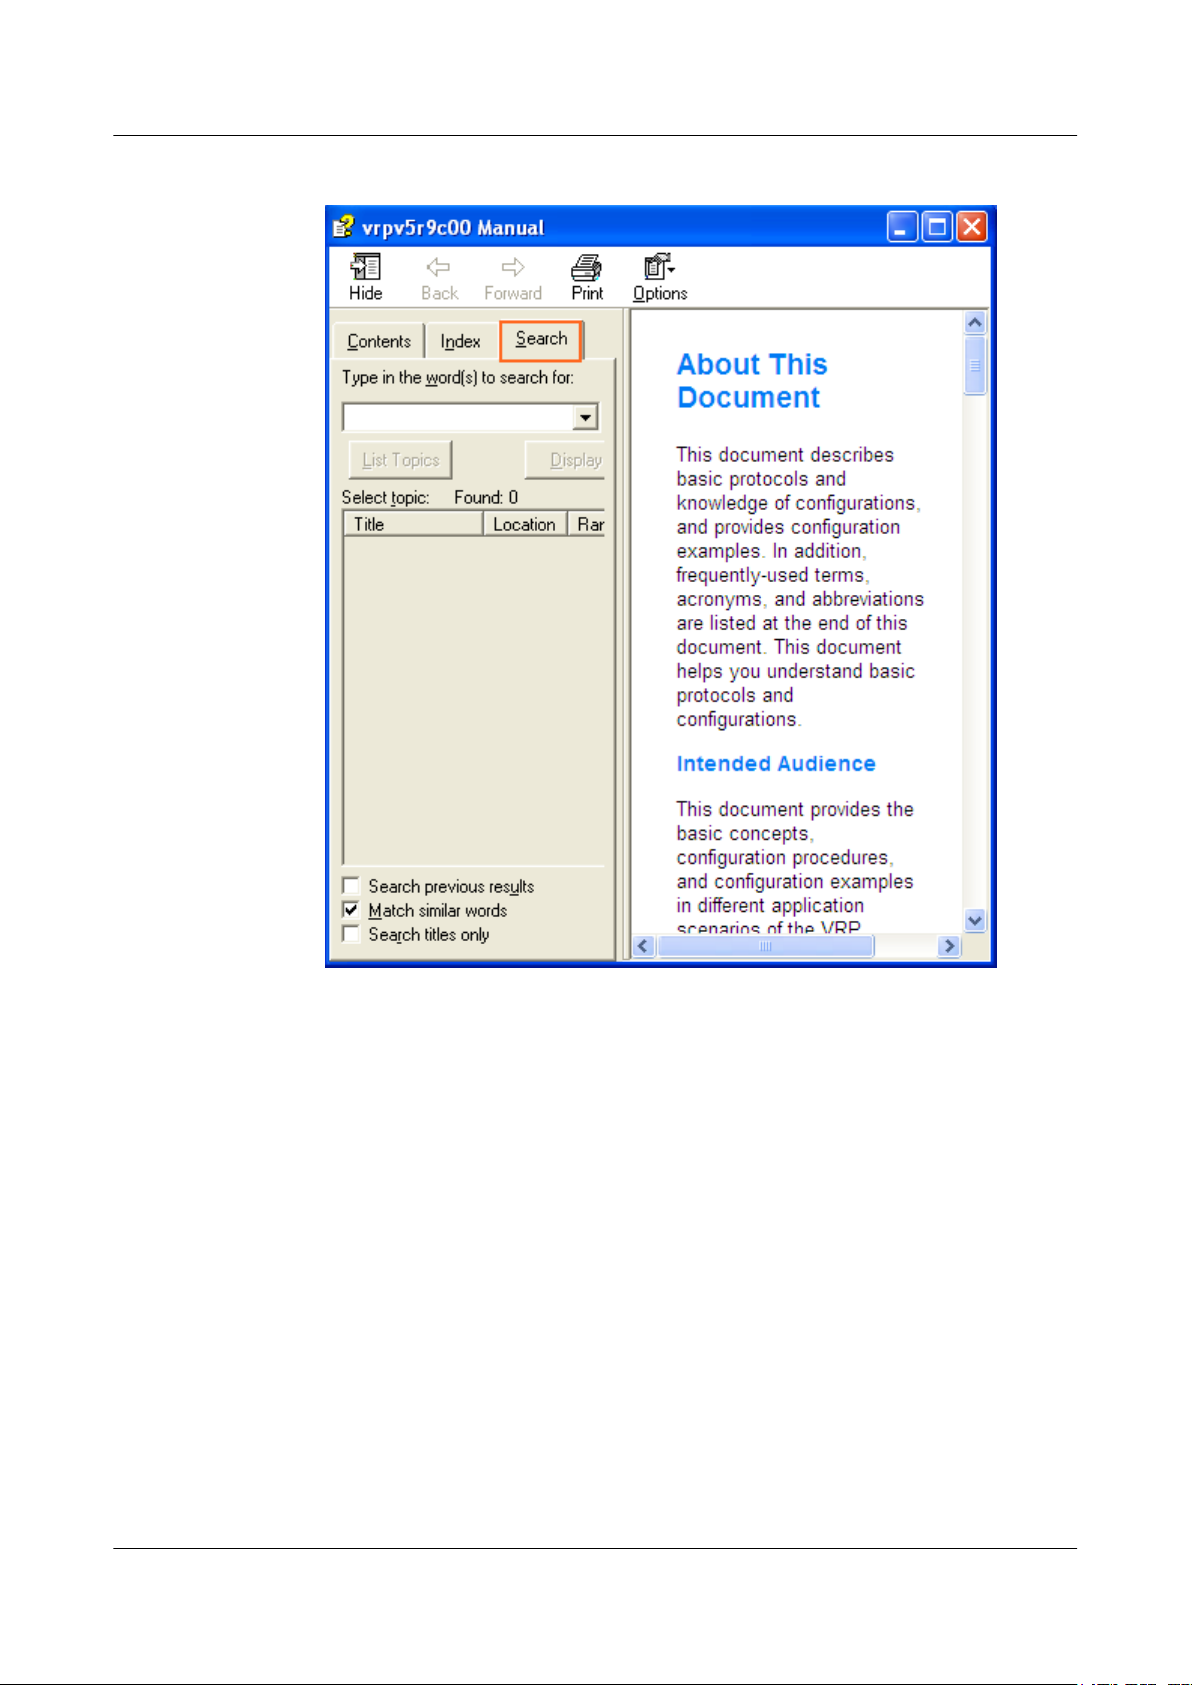
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Figure 2-1 Entering the search window
3. Enter a desired command level in the "Type in the word(s) to search for" textbox and click
"List Topics". All commands of the specified level will be displayed as shown in Figure
2-2.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
10
Page 26
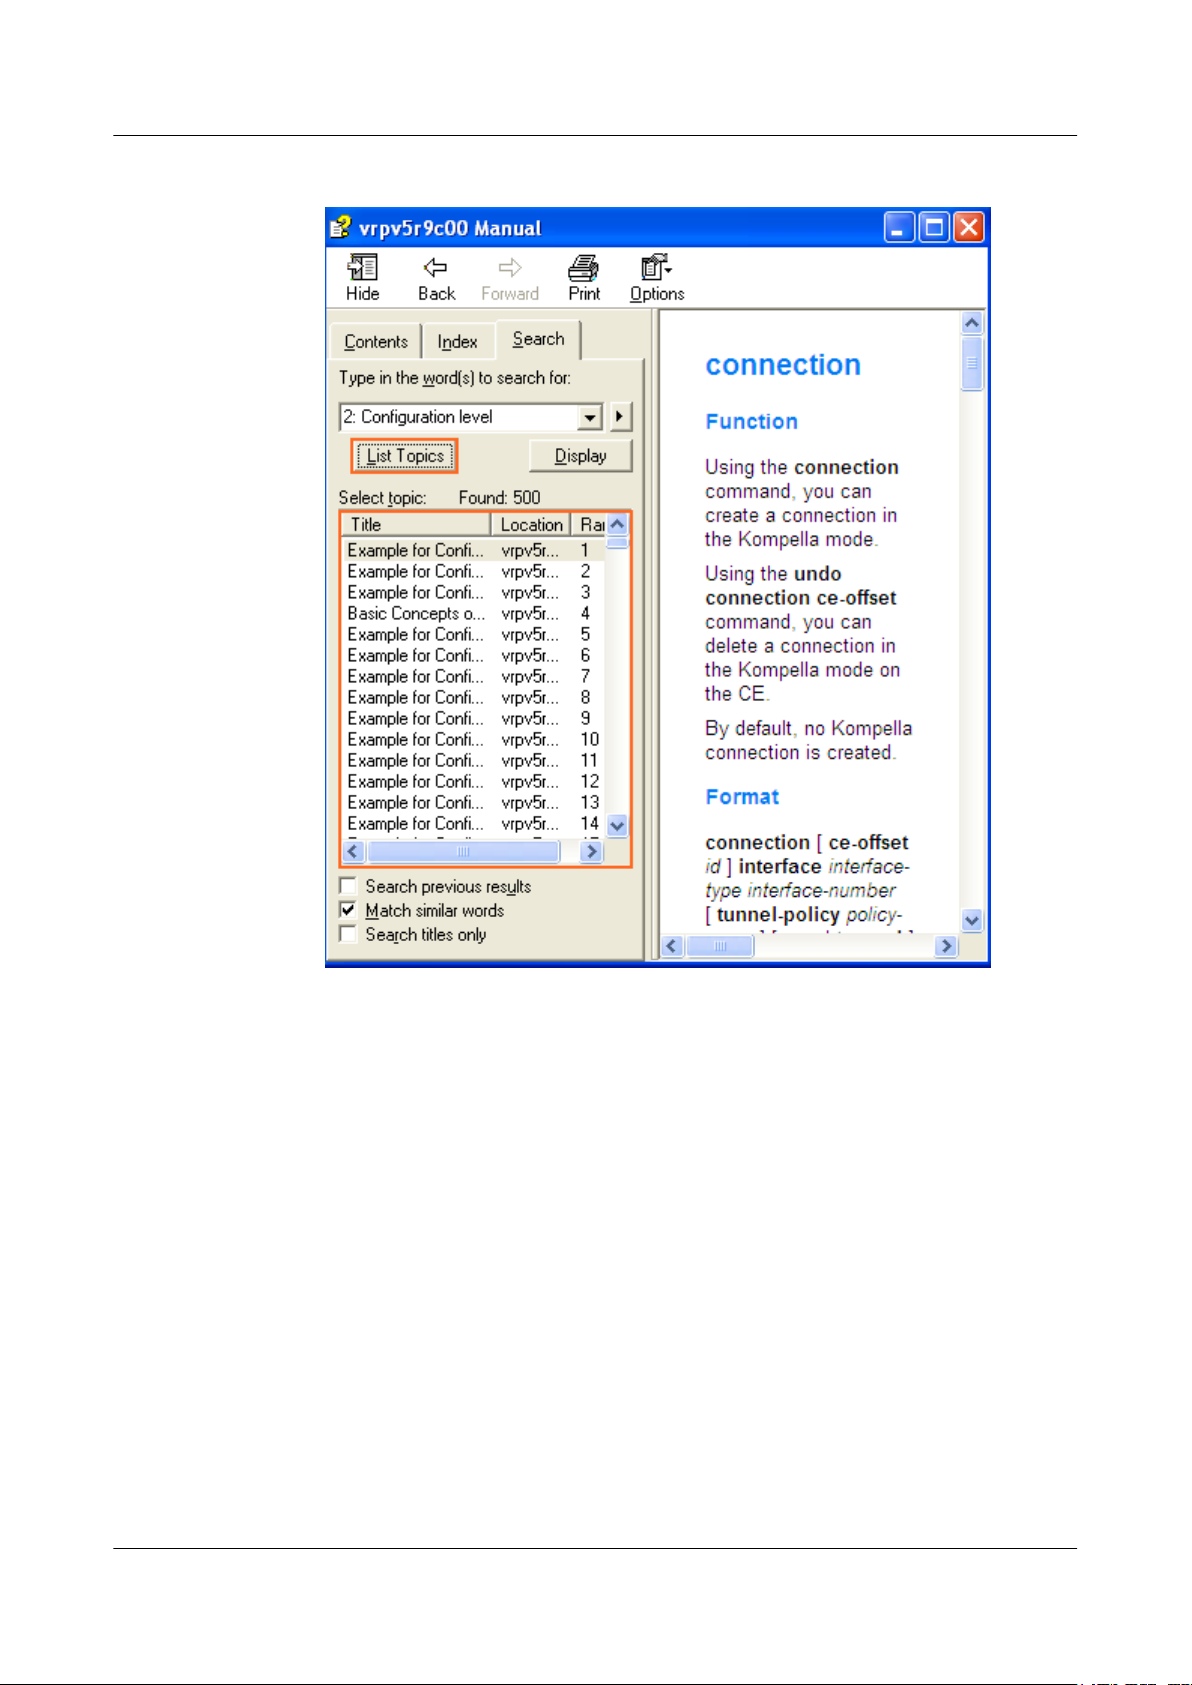
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Figure 2-2 Searching commands based on a specific level
2.1.3 Command Line Views
The command line interface has different command views. All the commands are registered in
one or more command views. You can run a command only when you enter the corresponding
command view.
The following part uses the user, system, and BFD views as an example:
# Establish connection to the router. If the router adopts the default configuration, you can enter
the user view with the prompt of <HUAWEI>.
<HUAWEI>
# Run the system-view command to enter the system view.
<HUAWEI> system-view
[HUAWEI]
# Run the aaa command in the system view to enter the AAA view.
[HUAWEI] aaa
[HUAWEI-aaa]
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
11
Page 27
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
NOTE
l The command prompt "HUAWEI" is the default host name.
l The prompt indicates a specific view. For example, "<HUAWEI>" indicates the user view, and
"[HUAWEI-ui-console0]" indicates the console user interface view.
Some commands can be used in both system and other views, but have different effects. For
example, the mpls command can be run in the system view to enable MPLS globally or in the
interface view to enable MPLS only on this interface.
2.2 Online Help
When inputting command lines or configuring services, you can use the online help function to
obtain real-time help.
2.2.1 Full Help
When inputting a command, you can use the full help function to obtain all keywords or
parameters of this command.
Procedure
l You can obtain the full help of a command line in the following manners.
– Enter a question mark (?) in any command line view to display all the commands and
their simple descriptions.
<HUAWEI> ?
User view commands:
arp-ping ARP-ping
backup Backup information
batch-cmd Batch commands
board-channel-check Board-Channel-Check enable/disable
capture-packet enable capturing packet
cd Change current directory
...
...
– Enter a command and a question mark (?) separated by a space. If the key word is at
this position, all key words and their simple descriptions are displayed. For example:
<HUAWEI> language-mode ?
Chinese Chinese environment
English English environment
Chinese and English are keywords; Chinese environment and English
environment describe the keywords respectively.
– Enter a command and a question mark (?) separated by a space, and if a parameter is at
this position, the related parameter names and parameter descriptions are displayed. For
example:
[HUAWEI] ftp timeout ?
INTEGER<1-35791> The value of FTP timeout (in minutes)
[HUAWEI] ftp timeout 35 ?
<cr> Please press ENTER to execute command
[HUAWEI] ftp timeout 35
In the preceding display, INTEGER<1-35791> describes the parameter value; The
value of FTP timeout (in minutes) is a simple description of the parameter usage;
<cr> indicates that no parameter is at this position. The command is repeated in the next
command line. You can press Enter to run the command.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
12
Page 28
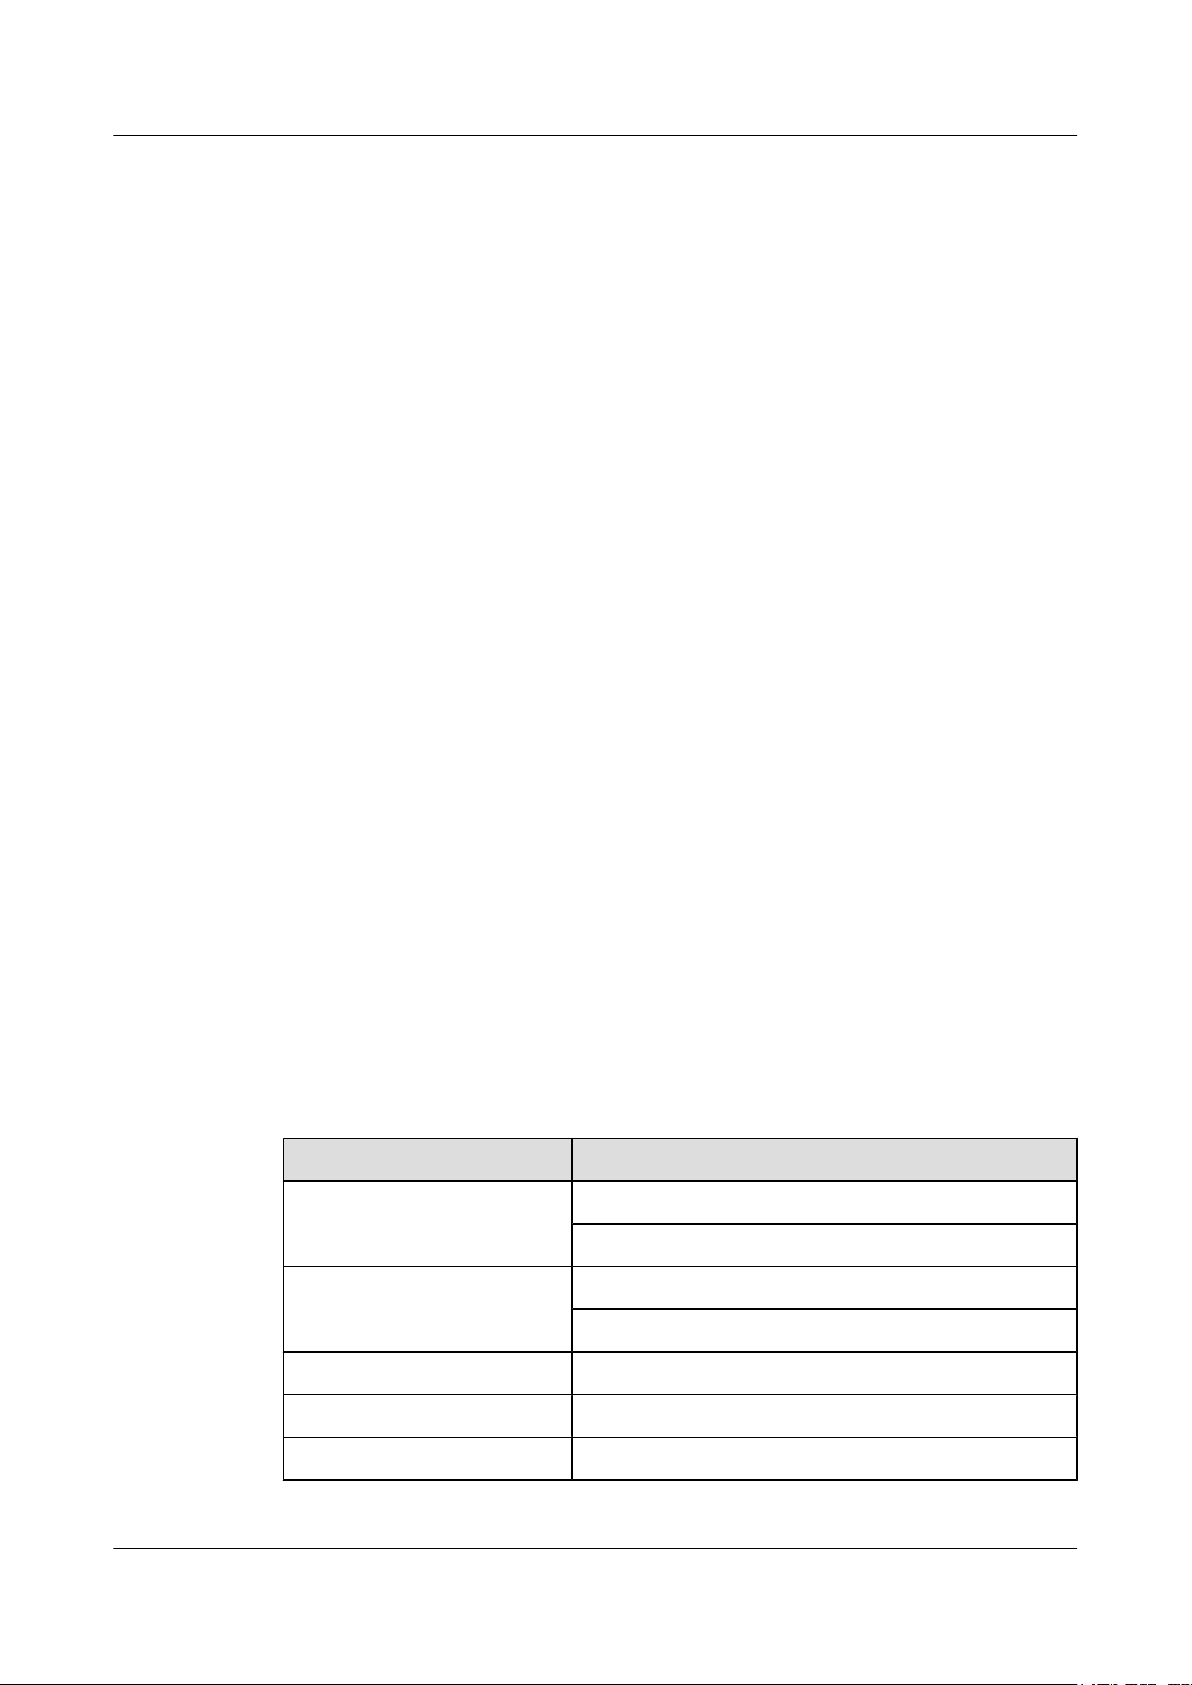
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2.2.2 Partial Help
If you enter only the first one or a few characters of a command, you can use the partial help
function to obtain all keywords following the character or character string.
Procedure
l You can obtain the partial help of a command line in the following manners.
– Enter a character string with a question mark (?) closely following it to display all
commands that begin with this character string.
<HUAWEI> d?
debugging delete
dir display
– Enter a command and a character string with a question mark (?) closely following it
to display all the key words that begin with this character string.
<HUAWEI> display b?
bas-interface bfd
bgp board-current
board-power board-type
bootmode-current bootmode-next
bootrom btv
buffer bulk-stat
– Enter the first several letters of a key word in the command and then press Tab to display
the complete key word on the condition that the letters uniquely identify the key word.
Otherwise, if you continue to press Tab, different key words are displayed. You can
select the needed key word.
----End
2.2.3 Error Messages of the Command Line Interface
If an entered command passes the syntax check, the system executes it. Otherwise, the system
prompts an error message.
All the commands entered by the user are run correctly, if the grammar check has been passed.
Otherwise, error messages are reported to the user. See Table 2-2 for the common error
messages.
Table 2-2 Common error messages of the command line
Error messages
Unrecognized command The command cannot be found
Wrong parameter Parameter type error
Incomplete command Incomplete command entered
Too many parameters Too many parameters entered
Cause of the error
The key word cannot be found
The parameter value exceeds the limit
Ambiguous command Indefinite parameters entered
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
13
Page 29
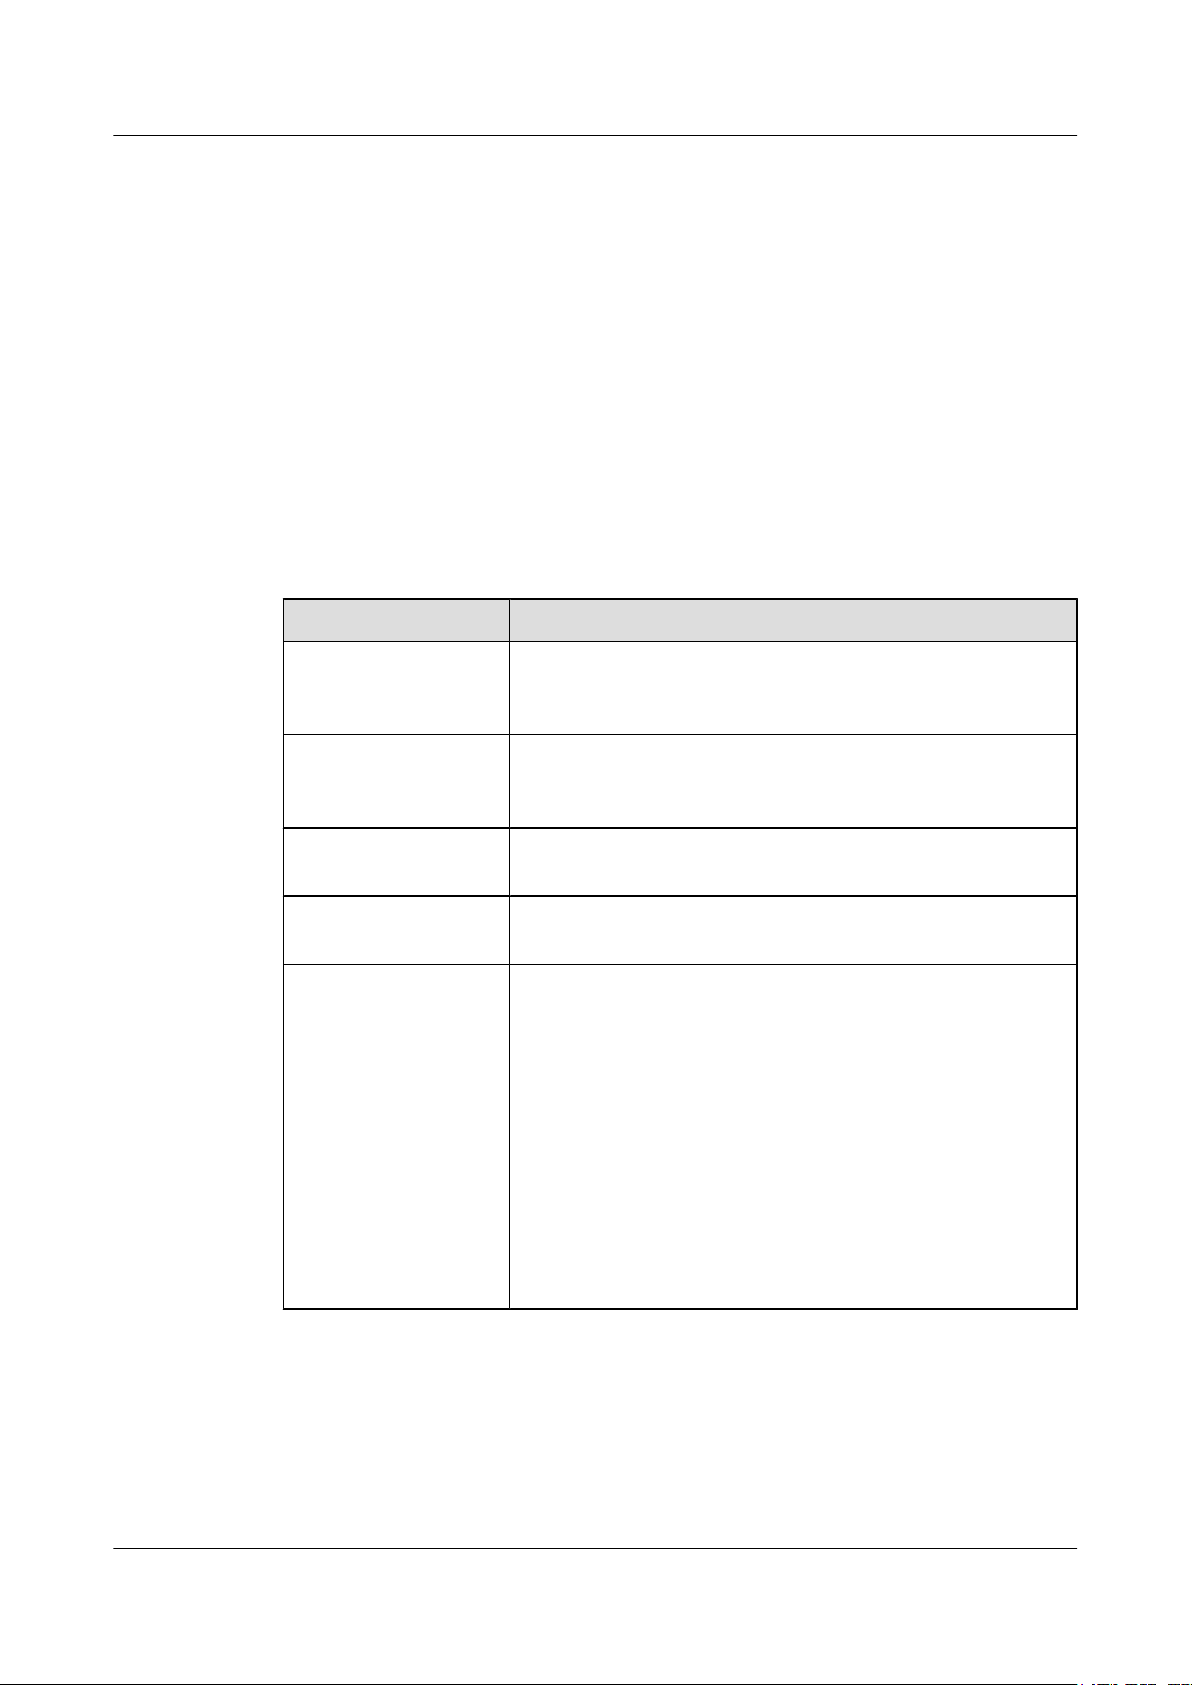
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2.3 CLI Features
The CLI provides the following features to help users flexibly use it.
2.3.1 Editing
The editing function of command lines helps you edit command lines or obtain help by using
certain keys.
The command line supports multi-line edition. The maximum length of each command is 512
characters.
Keys for editing that are often used are shown in Table 2-3.
Table 2-3 Keys for editing
Key Function
Common key Inserts a character in the current position of the cursor if the editing
buffer is not full and the cursor moves to the right. Otherwise, an
alarm is generated.
Backspace Deletes the character on the left of the cursor that moves to the
left. When the cursor reaches the head of the command, an alarm
is generated.
Left cursor key ← or
Ctrl_B
Right cursor key → or
Ctrl_F
Tab Press Tab after typing the incomplete key word and the system
Moves the cursor to the left by the space of a character. When the
cursor reaches the head of the command, an alarm is generated.
Moves the cursor to the right by the space of a character. When
the cursor reaches the end of the command, an alarm is generated.
runs the partial help:
l If the matching key word is unique, the system replaces the
typed one with the complete key word and displays it in a new
line with the cursor a space behind.
l If there are several matches or no match at all, the system
displays the prefix first. Then you can press Tab to view the
matching key word one by one. In this case, the cursor closely
follows the end of the word and you can type a space to enter
the next word.
l If a wrong key word is entered, press Tab and the word is
displayed in a new line.
2.3.2 Displaying
All command lines have the same displaying feature. You can construct the displaying mode as
required.
You can control the display of information on the CLI as follows:
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
14
Page 30
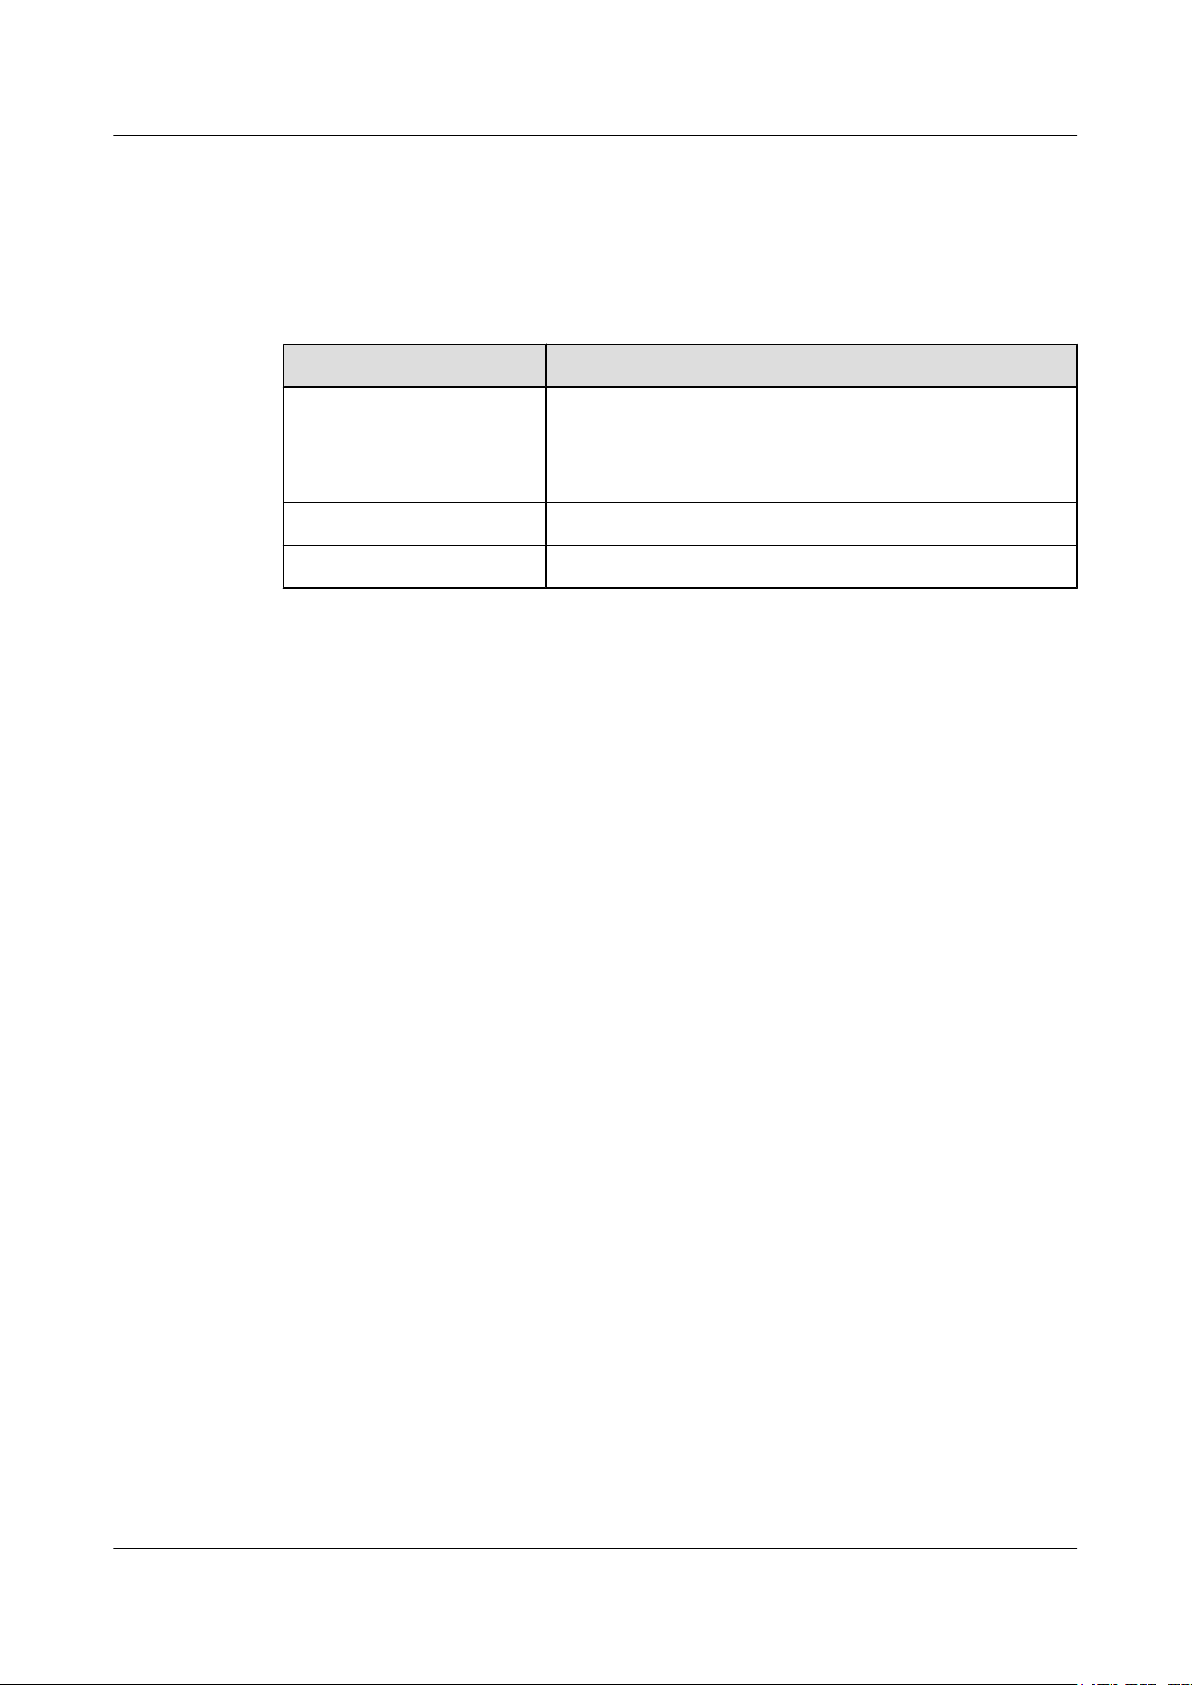
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
l Prompts and help information can be displayed in both Chinese and English. You can use
the language-mode language-name command to change the language mode.
l If output information cannot be displayed on a full screen, you have three options to view
the information, as shown in Table 2-4.
Table 2-4 Keys for displaying
Key Function
Ctrl_C Stops the display and running of the command.
NOTE
You can also press any of the keys except the spacebar and Enter key
to stop the display and running of the command.
Space Allows information to be displayed on the next screen.
Enter Allows information to be displayed on the next line.
2.3.3 Regular Expressions
The regular expression is an expression that describes a set of strings. It consists of common
characters (such as letters from "a" to "z") and particular characters (also named metacharacters).
The regular expression is a template according to which you can search for the required string.
Users can use regular expressions to filter output information to rapidly locate desired
information.
A regular expression can provide the following functions:
l Searching for and obtaining a sub-string that matches a rule in the string.
l Substituting a string according to a certain matching rule.
Formal Language Theory of the Regular Expression
The regular expression consists of common characters and particular characters.
l Common characters
Common characters are used to match themselves in a string, including all upper-case and
lower-case letters, digits, punctuation, and special symbols. For example, a matches the
letter "a" in "abc", 202 matches the digit "202" in "202.113.25.155", and @ matches the
symbol "@" in "[email protected]".
l Particular characters
Particular characters are used together with common characters to match the complex or
particular string combination. Table 2-5 describes particular characters and their syntax.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
15
Page 31
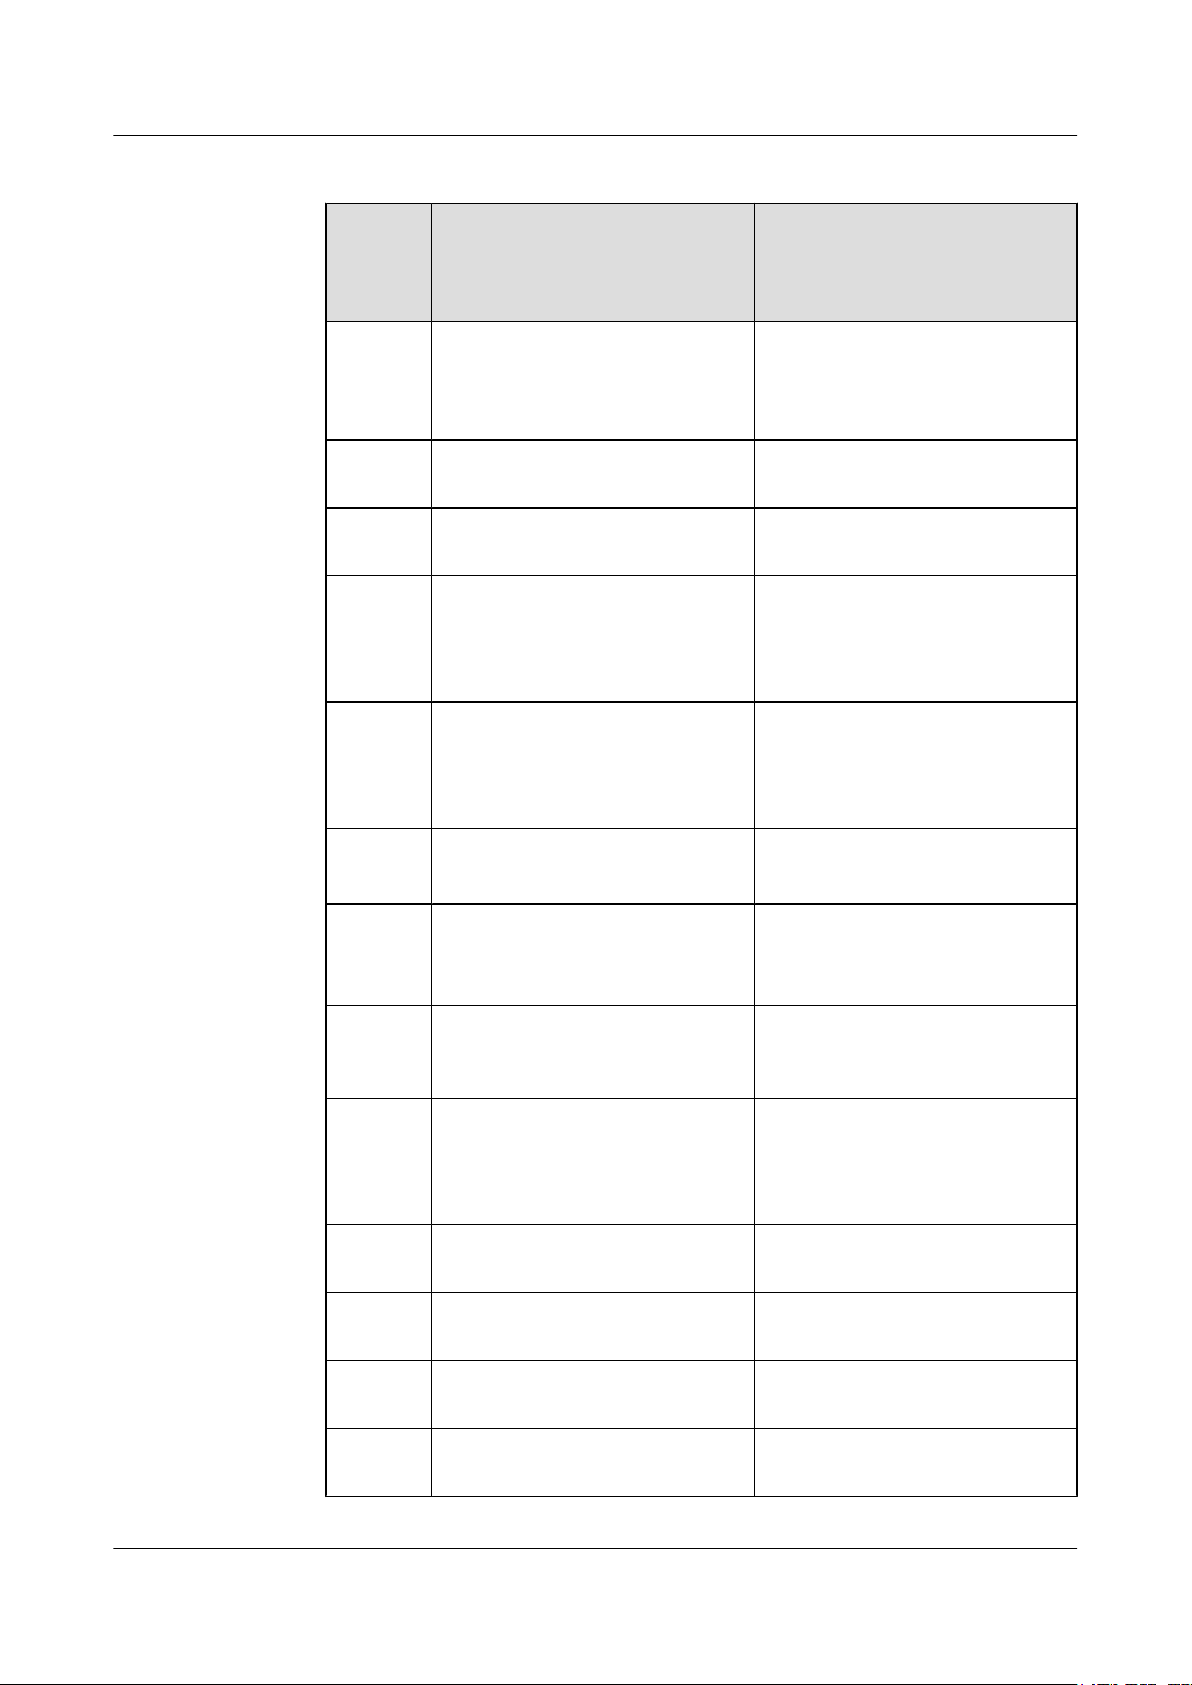
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Table 2-5 Description of particular characters
Particul
Syntax Example
ar
characte
r
\ Defines an escape character, which
is used to mark the next character
(common or particular) as the
common character.
^ Matches the starting position of the
string.
$ Matches the ending position of the
string.
* Matches the preceding element zero
or more times.
+ Matches the preceding element one
or more times
\* matches "*".
^10 matches "10.10.10.1" instead of
"20.10.10.1".
1$ matches "10.10.10.1" instead of
"10.10.10.2".
10* matches "1", "10", "100", and
"1000".
(10)* matches "null", "10", "1010",
and "101010".
10+ matches "10", "100", and
"1000".
(10)+ matches "10", "1010", and
"101010".
? Matches the preceding element zero
or one time.
10? matches "1" and "10".
(10)? matches "null" and "10".
. Matches any single character. 0.0 matches "0x0" and "020".
.oo matches "book", "look", and
"tool".
() Defines a subexpression, which can
be null. Both the expression and the
100(200)+ matches "100200" and
"100200200".
subexpression should be matched.
x|y Matches x or y. 100|200 matches "100" or "200".
1(2|3)4 matches "124" or "134",
instead of "1234", "14", "1224", and
"1334".
[xyz] Matches any single character in the
regular expression.
[^xyz] Matches any character that is not
contained within the brackets.
[a-z] Matches any character within the
specified range.
[123] matches the character 2 in
"255".
[^123] matches any character except
for "1", "2", and "3".
[0-9] matches any character ranging
from 0 to 9.
[^a-z] Matches any character beyond the
specified range.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
[^0-9] matches all non-numeric
characters.
16
Page 32
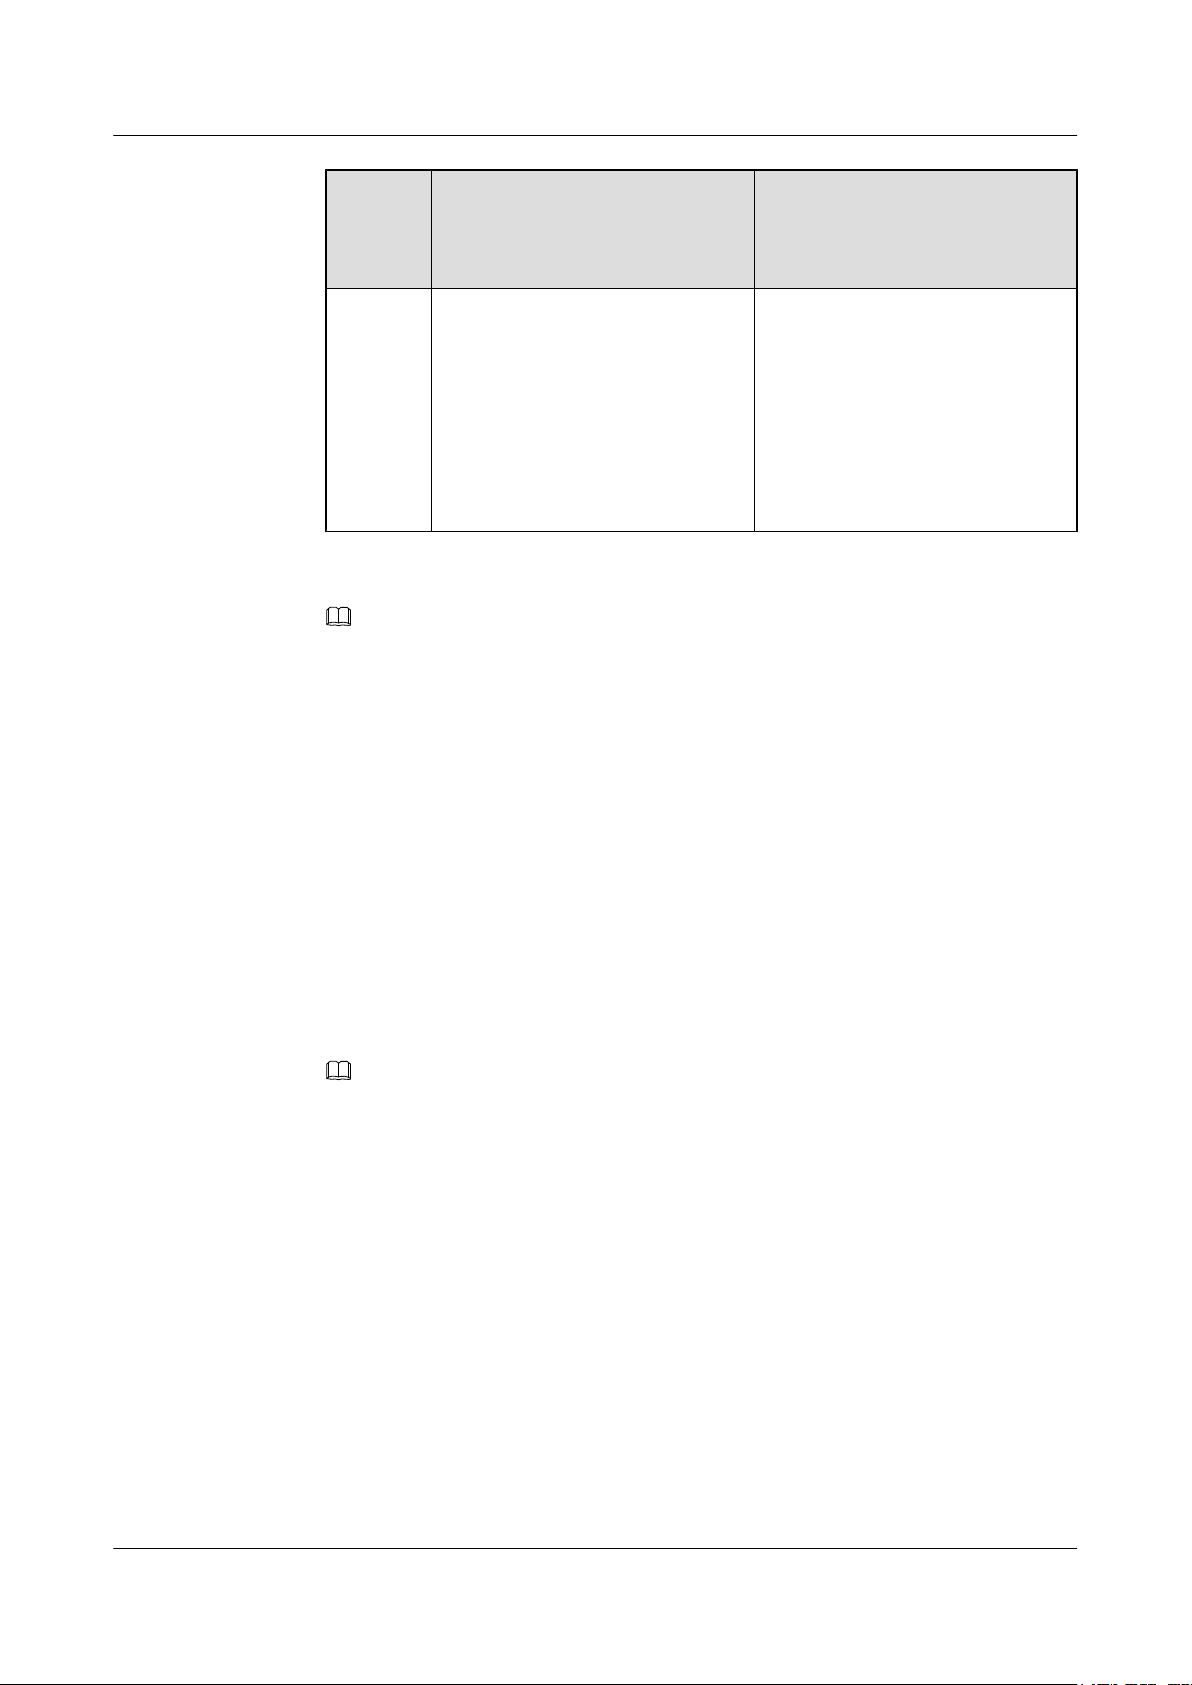
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Particul
Syntax Example
ar
characte
r
_ Matches a comma "," left brace "{",
right brace "}", left parenthesis "(",
and right parenthesis ")".
Matches the starting position of the
_2008_ matches "2008", "space
2008 space", "space 2008", "2008
space", ",2008,", "{2008}",
"(2008)", "{2008", and "(2008}".
input string.
Matches the ending position of the
input string.
Matches a space.
NOTE
Unless otherwise specified, all characters in the preceding table are displayed on the screen.
l Degeneration of particular characters
Certain particular characters, when being placed at the following positions in the regular
expression, degenerate to common characters.
– The particular characters following "\" is transferred to match particular characters
themselves.
– The particular characters "*", "+", and "?" placed at the starting position of the regular
expression. For example, +45 matches "+45" and abc(*def) matches "abc*def".
– The particular character "^" placed at any position except for the start of the regular
expression. For example, abc^ matches "abc^".
– The particular character "$" placed at any position except for the end of the regular
expression. For example, 12$2 matches "12$2".
– The right bracket such as ")" or "]" being not paired with its corresponding left bracket
"(" or "[". For example, abc) matches "abc)" and 0-9] matches "0-9]".
NOTE
Unless otherwise specified, degeneration rules are applicable when preceding regular expressions
serve as subexpressions within parentheses.
l Combination of common and particular characters
In actual application, a regular expression combines multiple common and particular
characters to match certain strings.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
17
Page 33
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Specifying a Filtering Mode in Command
CAUTION
The HUAWEI NetEngine80E/40E uses a regular expression to implement the filtering function
of the pipe character. A display command supports the pipe character only when there is
excessive output information.
When the output information is queried according to the filtering conditions, the first line of the
command output starts with the information containing the regular expression.
The command can carry the parameter | count to display the number of matching entries. The
parameter | count can be used together with other parameters.
For the commands supporting regular expressions, the three filtering methods are as follows:
l | begin regular-expression: displays the information that begins with the line that matches
regular expression.
l | exclude regular-expression: displays the information that excludes the lines that match
regular expression.
l | include regular-expression: displays the information that includes the lines that match
regular expression.
NOTE
The value of regular-expression is a string of 1 to 255 characters.
Specify a Filtering Mode when Information is Displayed
When a lot of information is displayed, you can specify a filtering mode in the prompt "---- More
----".
l /regular-expression: displays the information that begins with the line that matches regular
expression.
l -regular-expression: displays the information that excludes lines that match regular
expression.
l +regular-expression: displays the information that includes lines that match regular
expression.
2.3.4 Previously-Used Commands
The CLI provides a function similar to DosKey to automatically save commands used previously
on the device. If you need to run a command that has been executed, you can call the command
from those have been used previously on the device. This facilitates user operation.
By default, the system saves a maximum of 10 previously-used commands for each user. You
can run the history-command max-size size-value command in the user view to set the number
of previously-used commands saved in the system. A maximum of 256 previously-used
commands can be saved in the system.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
18
Page 34
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
NOTE
Setting the number of saved previously-used commands to a proper value is recommended. If a large
number of previously-used commands are saved, it will take a long time to locate a needed previouslyused command, affecting efficiency.
The operations are shown in Table 2-6
Table 2-6 Access the previously-used commands
Action Key or Command Result
Display
previously-
display historycommand
Display previously-used commands entered by
users.
used
commands.
Access the last
previouslyused
Up cursor key (↑) or
Ctrl_P
Display the last previously-used command if there
is an earlier previously-used command. Otherwise,
an alarm is generated.
command.
Access the next
previouslyused
Down cursor key
(↓) or Ctrl_N
Display the next previously-used command if there
is a later previously-used command. Otherwise, the
command is cleared and an alarm is generated.
command.
NOTE
On the HyperTerminal of Windows 9X, cursor key ↑ is invalid as the HyperTerminals of Windows 9X
define the keys differently. In this case, you can replace the cursor key ↑ with Ctrl_P.
When you use previously-used commands, note the following points:
l The saved previously-used commands are the same as that those entered by users. For
example, if the user enters an incomplete command, the saved command also is incomplete.
l If the user runs the same command several times, the earliest command is saved. If the
command is entered in different forms, they are considered as different commands.
For example, if the display ip routing-table command is run several times, only one
previously-used command is saved. If the disp ip routing command and the display ip
routing-table command are run, two previously-used commands are saved.
2.3.5 Batch Command Execution
If multiple commands are frequently used consecutively, you can edit these commands to be
executed in batches. This simplifies command input and improves efficiency.
Procedure
Step 1 In the user view, run:
batch-cmd edit
Commands are edited to be executed in batches.
The batch-cmd edit command can be used by only one user at a time.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
19
Page 35
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
The maximum length of a command (including the incomplete command) to be entered is 512
characters.
When editing commands, press Enter to complete the editing of each command.
NOTE
l After the batch-cmd edit command is run successfully to edit the commands to be executed in batches,
the system deletes the original commands to be run in batches.
l The commands that are already edited are saved in memory and are deleted for ever when the system
is restarted.
Step 2 After all commands are edited, you can press the shortcut buttons Ctrl_Z to exit the editing state
and return to the user view.
Step 3 In the user view, run:
batch-cmd execute
The commands are executed in batches.
The batch-cmd execute command can be used by only one user at a time.
The sequence of running commands is the same as the sequence of editing commands. You can
view the execution of these commands on the CLI. After the execution is complete, the user
view is displayed.
NOTE
If the batch-cmd edit or batch-cmd execute command is among the commands to be executed in batches,
the system displays an error when executing the batch-cmd edit or batch-cmd execute command and
continues to execute the following commands.
----End
2.4 Shortcut Keys
Using the system or user-defined shortcut keys makes it easier to enter commands.
2.4.1 Classifying Shortcut Keys
There are two types of shortcut keys, namely, system shortcut keys and user-defined shortcut
keys. Familiarize yourself with shortcut keys so as to use them accurately.
The shortcut keys in the system are classified into the following types:
l User-defined shortcut keys: CTRL_G, CTRL_L, CTRL_O, and CTRL_U. The user can
correlate these shortcut keys with any commands. When the shortcut keys are pressed, the
system automatically runs the corresponding command. For details of defining the shortcut
keys, see 2.4.2 Defining Shortcut Keys.
l System-defined shortcut keys: These shortcut keys with fixed functions are defined by the
system. Table 2-7 lists the system-defined shortcut keys.
NOTE
Different terminal software defines these keys differently. Therefore, the shortcut keys on the terminal may
be different from those listed in this section.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
20
Page 36
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
Table 2-7 System-defined shortcut keys
Key Function
CTRL_A The cursor moves to the beginning of the current line.
CTRL_B The cursor moves to the left by the space of a character.
CTRL_C Terminates the running function.
CTRL_D Deletes the character where the cursor lies.
CTRL_E The cursor moves to the end of the current line.
CTRL_F The cursor moves to the right by the space of a character.
CTRL_H Deletes one character on the left of the cursor.
CTRL_K Stops the creation of the outbound connection.
CTRL_N Displays the next command in the previously-used command
buffer.
CTRL_P Displays the previous command in the previously-used
command buffer.
CTRL_R Repeats the display of the information of the current line.
CTRL_T Terminates the outbound connection.
CTRL_V Pastes the contents on the clipboard.
CTRL_W Deletes a character string or character on the left of the cursor.
CTRL_X Deletes all the characters on the left of the cursor.
CTRL_Y Deletes all the characters on the place of the cursor and the right
of the cursor.
CTRL_Z Returns to the user view.
CTRL_] Terminates the inbound or redirection connections.
ESC_B The cursor moves to the left by the space of a word.
ESC_D Deletes a word on the right of the cursor.
ESC_F The cursor moves to the right to the end of next word.
ESC_N The cursor moves downward to the next line.
ESC_P The cursor moves upward to the previous line.
ESC_SHIFT_< Sets the position of the cursor to the beginning of the clipboard.
ESC_SHIFT_> Sets the position of the cursor to the end of the clipboard.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
21
Page 37
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2.4.2 Defining Shortcut Keys
If one or multiple commands are frequently used, you can correlate these commands with
shortcut keys. This facilitates user operation and improves efficiency. Only management-level
users have the rights to define shortcut keys.
Configure as follows in the system view.
Action Command
Define shortcut keys hotkey { CTRL_G | CTRL_L | CTRL_O | CTRL_U }
command-text
NOTE
When defining the shortcut keys, use double quotation marks to define the command if this command
contains several commands words, that is, if spaces exist in the command.
By default, CTRL_G, CTRL_L and CTRL_O correspond to the following commands
respectively:
l CTRL_G: display current-configuration
l CTRL_L: display ip routing-table
l CTRL_O: undo debugging all
By default, CTRL_U is not correlated with any command.
2.4.3 Use of Shortcut Keys
You can use the shortcut key at any position that allows a command to be entered. The system
executes an entered shortcut key and displays the corresponding command on the screen in the
same way as you enter a complete command.
l If you have typed part of a command and have not pressed Enter, you can press the shortcut
keys to clear the entered command and display the full corresponding command. This
operation has the same effect as that of deleting all commands and then re-entering the
complete command.
l The shortcut keys are run as the commands, the syntax is recorded to the command buffer
and log for fault location and querying.
NOTE
The terminal in use may affect the functions of the shortcut keys. For example, if the customized shortcut
keys of the terminal conflict with those of the router, the input shortcut keys are captured by the terminal
program and hence the shortcut keys do not function.
Run the following command in any view to display the use of shortcut keys.
Action
Command
Check the usage of shortcut keys. display hotkey
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
22
Page 38
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
2.5 Configuration Examples
This section provides several examples for using command lines.
2.5.1 Example for Running Commands in Batches
This part provides an example for running commands in batches. In this example, by editing the
commands to be run in batches, you can configure the system to automatically run the commands
in batches.
Context
If commands are frequently used consecutively, especially a large number of commands, you
can run the commands in batches to improve efficiency.
For example, during the preventive maintenance inspection (PMI), you can run commands in
batches. That is, enter all PMI commands once and then send all the command output information
to the PMI tool, which can improve the PMI efficiency.
Procedure
Step 1 Edit the display users, display startup, and display clock commands to be run in batches.
Step 2 Run the commands in batches.
Log in to the router and do as follows:
<HUAWEI> batch-cmd edit
Info: Begin editing batch commands. Press "Ctrl+Z" to abort this session.
display users
display startup
display clock
<HUAWEI>
<HUAWEI> batch-cmd execute
<HUAWEI>batch-cmd execute command: display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
35 VTY 1 00:00:00 TEL 190.120.2.19 no
Username : Unspecified
<HUAWEI>batch-cmd execute command: display startup
MainBoard:
Configured startup system software: cfcard:/V600R003C00SPC300.cc
Startup system software: cfcard:/V600R003C00SPC300.cc
Next startup system software: cfcard:/V600R003C00SPC300.cc
Startup saved-configuration file: cfcard:/vrp.cfg
Next startup saved-configuration file: cfcard:/vrp.cfg
Startup paf file: default
Next startup paf file: default
Startup license file: default
Next startup license file: default
Startup patch package: NULL
Next startup patch package: NULL
<HUAWEI>
batch-cmd execute command: display clock
2011-01-27 01:25:24
Thursday
Time Zone(DefaultZoneName) : UTC
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
23
Page 39
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
<HUAWEI>
batch-cmd execute finished.
----End
2.5.2 Example for Using Tab
This example shows how to use the Tab key. After inputting an incomplete keyword, you can
press Tab and obtain all related keywords or verify the correctness of the input keyword.
Context
Usually, you do not need to input complete keywords. Instead, you can just input one or a few
beginning characters of a keyword and press Tab to complete the keyword. The Tab key helps
search for and use commands.
Procedure
l Tab can be used in three ways as shown in the following example.
– The matching key word is unique after the incomplete key word is input.
1. Input the incomplete key word.
[HUAWEI] info-
2. Press Tab.
The system replaces the input one with the complete key word and displays it in a
new line with the cursor leaving a space behind.
[HUAWEI] info-center
– There are several matches or no match after the incomplete key word is input.
# info-center can be followed by three key words.
[HUAWEI] info-center log?
logbuffer logfile loghost
1. Input the incomplete key word.
[HUAWEI] info-center l
2. Press Tab.
The system displays the prefix first. The prefix in this example is "log".
[HUAWEI] info-center log
Continue to press Tab. The cursor is closely following the end of the word.
[HUAWEI] info-center loghost
[HUAWEI] info-center logbuffer
[HUAWEI] info-center logfile
Stop pressing Tab after the key word logfile that you need is displayed.
3. Input a space to enter the next word channel.
[HUAWEI] info-center logfile channel
– Input an incorrect keyword and press Tab to check the correctness of the keyword.
1. Input a wrong keyword loglog.
[HUAWEI] info-center loglog
2. Press Tab.
[HUAWEI] info-center loglog
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
24
Page 40
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
The system displays information in a new line, but the keyword loglog remains
unchanged and there is no space between the cursor and the keyword, indicating
that this keyword is inexistent.
----End
2.5.3 Example for Using Shortcut Keys
This example shows how to use shortcut keys. In this example, frequently-used commands are
correlated with shortcut keys. You can press the shortcut keys instead of inputting the commands.
This facilitates user operation and improves efficiency.
Context
If the login router is defined with shortcut keys, the shortcut keys can be used by any user
regardless of the user level.
Procedure
Step 1 Correlate Ctrl_U with the display ip routing-table command and run the shortcut keys.
<HUAWEI> system-view
[HUAWEI] hotkey ctrl_u "display ip routing-table"
NOTE
When defining shortcut keys for a command, use double quotation marks to quote the command if the
command consisting of multiple words, which are separated by spaces. No double quotation marks are
required for single-word commands.
Step 2 Press Ctrl_U when the prompt [HUAWEI] appears.
[HUAWEI] display ip routing-table
Route Flags: R - relay, D - download to fib
-----------------------------------------------------------------------------Routing Tables: Public
Destinations : 8 Routes : 8
Destination/Mask Proto Pre Cost Flags NextHop Interface
51.51.51.9/32 Direct 0 0 D 127.0.0.1 InLoopBack0
100.2.0.0/16 Direct 0 0 D 100.2.150.51 GigabitEthernet0/
0/0
100.2.150.51/32 Direct 0 0 D 127.0.0.1 InLoopBack0
100.2.255.255/32 Direct 0 0 D 127.0.0.1 InLoopBack0
127.0.0.0/8 Direct 0 0 D 127.0.0.1 InLoopBack0
127.0.0.1/32 Direct 0 0 D 127.0.0.1 InLoopBack0
127.255.255.255/32 Direct 0 0 D 127.0.0.1 InLoopBack0
255.255.255.255/32 Direct 0 0 D 127.0.0.1 InLoopBack0
---------------------------------------------------------------------
----End
2.5.4 Example for Copying Commands Using Shortcut Keys
This example shows how to copy commands by using shortcut keys. In this example, after a
specified command is copied by using shortcut keys, you can use the shortcut keys
Ctrl_Shift_V to paste the command.
Context
If you need to repeatedly run a command, you can use shortcut keys to copy the command.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
25
Page 41
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 2 CLI Overview
The copied command is saved on the clipboard and is available for only the current logged-in
user. After the user logs out of the router, the clipboard is cleared.
You can use shortcut keys to copy a command in any view.
Procedure
Step 1 Move the cursor to the beginning of the command and press Esc_Shift_<. Move the cursor to
the end and press Esc_Shift_>.
<HUAWEI> display ip routing-table
Step 2 Run the display clipboard command to view the contents on the clipboard.
<HUAWEI> display clipboard
---------------- CLIPBOARD----------------display ip routing-table
Step 3 Enter the command in any view, and press Ctrl_Shift_V to paste the contents of clipboard.
<HUAWEI> display ip routing-table
NOTE
If you press shortcut keys to copy a new command, you can paste only the new command by using shortcut
keys.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
26
Page 42
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
3 Basic Configuration
About This Chapter
This chapter describes how to configure the router to follow your using habits and the actual
environment requirements after logging in to the router.
3.1 Configuring the Basic System Environment
This section describes how to configure the basic system environment.
3.2 Displaying System Status Messages
This section describes how to use display commands to check basic configurations of the current
system.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
27
Page 43
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
3.1 Configuring the Basic System Environment
This section describes how to configure the basic system environment.
3.1.1 Establishing the Configuration Task
Before configuring the basic system environment, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This can help
you complete the configuration task quickly and accurately.
Applicable Environment
Before configuring services, you need to configure the basic system environment (such as the
language mode, time, device name, login information, and command level) to meet the
environment requirement.
Pre-configuration Tasks
Before configuring the basic system environment, complete the following task:
l Powering on the router
Data Preparation
To configure the basic system environment, you need the following data.
No.
1 Language mode
2 System time
3 Host name
4 Login information
5 Command level
Data
3.1.2 Switching the Language Mode
You can switch between the Chinese mode and the English mode as needed.
Context
After the language mode is switched, the system displays prompts and outputs of command lines
in the specified language.
Language information (Chinese and English) has been stored in the system software and does
not need to be loaded.
Do as follows in the user view:
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
28
Page 44
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
Procedure
l Run:
language-mode { chinese | english }
The language mode is switched.
By default, the English mode is used.
The help information on the router can be in English or in Chinese. The language mode is
stored in the system software and does not need to be loaded.
----End
3.1.3 Configuring the Equipment Name
When multiple devices on the network need to be managed, you can identify them by setting an
equipment name for each device.
Context
The new equipment name takes effect immediately.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
sysname host-name
The equipment name is set.
By default, the equipment name of the router is HUAWEI.
You can change the name of the router that appears in the command prompt.
----End
3.1.4 Setting the System Clock
You need to set the system time properly to ensure the cooperation between the NE80E/40E and
other devices.
Context
The system clock displays the current time and date of the system, time zone to which the system
belongs, and daylight saving time. The NE80E/40E supports the configurations of the time zone
and the daylight saving time.
Do as follows in the user view:
Procedure
Step 1 Run:
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
29
Page 45
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
clock datetime [ utc ] HH:MM:SS YYYY-MM-DD
The current date and time is set.
Step 2 Run:
clock timezone time-zone-name { add | minus } offset
The time zone is set.
l If add is configured, the current time is the UTC time plus the time offset. That is, the default
UTC time plus offset is equal to the time of time-zone-name.
l If minus is configured, the current time is the UTC time minus the time offset. That is, the
default UTC time minus offset is equal to the time of time-zone-name.
NOTE
UTC stands for the Universal Time Coordinated.
Step 3 Run:
clock daylight-saving-time time-zone-name one-year start-time start-date end-time
end-date offset
or
clock daylight-saving-time time-zone-name repeating start-time { { first | second
| third | fourth | last } weekday month | start-date } end-time { { first |
second | third | fourth | last } weekday month | end-date } offset [ start-year
[ end-year ] ]
The daylight saving time is set.
By default, the daylight saving time is not set.
During the configuration of the daylight saving time, you can configure the starting time and
ending time in one of the following modes: date+date, week+week, date+week, and week+date.
For details, see clock daylight-saving-time.
CAUTION
When the device is upgraded from an earlier version to the V600R003C00 version, the
configured daylight saving time does not take effect and needs to be reconfigured.
----End
3.1.5 Configuring a Header
If you need to provide information for users logging in, you can configure a header that the
system displays during or after login.
Context
A header text is a message displayed by the system when and after a user is logging in to the
router.
If you need to provide information for login users, you can configure a header that the system
displays during login or after login.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
30
Page 46
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
header login { information text | file file-name }
The header displayed during login is set.
Step 3 Run:
header shell { information text | file file-name }
The header displayed after login is set.
To display the header when the terminal connection has been activated but the user is not being
authenticated, configure the parameter login.
To display the header after the user logs in successfully, configure the parameter shell.
If the user can log in to the router without authentication, the system directly displays the header
after the login.
CAUTION
l The header text starts and ends with the same character. After a character is input and
Enter is pressed, an interactive interface is displayed. You can input the required information
ended with the first character. The system then exits from the interactive interface.
l If a user logs in to the router by using SSH1.X, the login header is not displayed during login,
but the shell header is displayed after login.
l If a user logs in to the router by using SSH2.0, both login and shell headers are displayed.
----End
3.1.6 Configuring Command Levels
This section describes how to configure command levels to ensure device security or allow lowlevel users to run high-level commands. By default, commands are registered in the sequence
of Level 0 to Level 3. If refined rights management is required, you can divide commands in to
16 levels, that is, from Level 0 to Level 15.
Context
If the user does not adjust a command level separately, after the command level is updated, all
originally-registered command lines adjust automatically according to the following rules:
l The commands of Level 0 and Level 1 remain unchanged.
l The commands of Level 2 are updated to Level 10 and the commands of Level 3 are updated
to Level 15.
l No command lines exist in Level 2 to Level 9 and Level 11 to Level 14. The user can adjust
the command lines to these levels separately to refine the management of privilege.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
31
Page 47
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
CAUTION
Changing the default level of a command is not recommended. If the default level of a command
is changed, some users may be unable to use the command any longer.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
command-privilege level rearrange
Update the command level in batches.
When no password is configured for a Level 15 user, the system prompts the user to set a superpassword for the level 15 user. At the same time, the system asks if the user wants to continue
with the update of command line level. Then, just select "N" to set a password. If you select "Y",
the command level can be updated in batches directly. This results in the user not logging in
through the Console port and failing to update the level.
Step 3 Run:
command-privilege level level view view-name command-key
The command level is configured. With the command, you can specify the level and view
multiple commands at one time (command-key).
All commands have default command views and levels. You do not need to reconfigure them.
----End
3.1.7 Configuring the Undo Command to Match in the Previous View Automatically
You can run the undo command in the current view and thus the system automatically matches
the previous view.
Context
If the user allows the undo command to automatically match the previous view and the user
runs the undo command that is not registered in the current view, the system searches the
undo command in the previous view.
CAUTION
The undo command has disadvantages due to automatically matching. For example, when the
user runs the undo ospf command in the interface view where the command is not registered,
the system searches in system view automatically. This may lead to global deletion of the OSPF
feature.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
32
Page 48
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
matched upper-view
The undo command is configured to match the upper level view.
By default, the undo command does not match the previous view automatically.
NOTE
l The matched upper-view command is valid for current login users who run this command.
l It is not recommended that you configure the undo command to automatically match the upper level
view, unless necessary.
----End
3.2 Displaying System Status Messages
This section describes how to use display commands to check basic configurations of the current
system.
Context
You can use the display commands to collect information about the system status. The display
commands are classified according to the following functions:
l Displays system configurations.
l Displays the running status of the system.
l Displays the diagnostic information about a system.
l Displays the restart information about the main control board.
See the related sections for display commands for protocols and interfaces. The following part
only shows the system-level display commands.
Run the following commands in any view.
3.2.1 Displaying System Configuration
This section describes how to check the system version, system time, original configuration, and
current configuration by using command lines.
Prerequisite
Basic configuration are complete.
Procedure
l Run the display version command to display the system version.
l Run the display clock [ utc ] command to display the system time.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
33
Page 49
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 3 Basic Configuration
l Run the display calendar command to display system calendar.
l Run the display saved-configuration command to display the original configuration.
l Run the display current-configuration command to display the current configuration.
NOTE
l The display version command can be used to display the software version of the system, the
chassis type, and the information about the main control board and interface board.
l The original configuration refers to information about configuration files used by the device when
the device has been powered on and is being initialized. The current configuration refers to the
configuration files taking effect during the device operation. For details, see the chapter
"Configuring System Startup" in the NE80E/40E Basic-Configuration.
----End
3.2.2 Displaying System Status
This section describes how to check the system operating status (the configuration of the current
view) by using command lines.
Prerequisite
Basic configurations are complete.
Procedure
l Run the display this command to display the configuration of the current view.
----End
3.2.3 Collecting System Diagnostic Information
This section describes how to collect information about all modules in the system.
Context
When the system fails to perform routine maintenance, you need to collect a lot of information
to locate faults. Then, you have to run different display commands to collect all information. In
this case, you can use the display diagnostic-information command to collect all information
about the current running modules in the system.
Procedure
l Run:
display diagnostic-information [ file-name ]
The system diagnosis information is displayed.
The display diagnostic-information command collects all information collected by
running the following commands, including display clock, display version, display cpu-
usage, display interface, display current-configuration, display saved-configuration,
display history-command, and so on.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
34
Page 50
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4 Configuring User Interface
About This Chapter
A user can log in to the router by using a console port or an AUX port, or by means of Telnet
or SSH (STelnet). For users logging in to router in different modes, the system uses different
user interfaces to manage the sessions between the router and the users.
4.1 User Interface Overview
The system supports console, AUX, and VTY user interfaces.
4.2 Configuring the Console User Interface
When a user logs in to the router by using a console port for local maintenance, you can configure
attributes for the corresponding console user interface are needed.
4.3 Configuring the AUX User Interface
When a user logs in to the router for local or remote configuration by using an AUX port,
configuring attributes in the corresponding AUX user interface is needed.
4.4 Configuring VTY User Interface
If you need to log in to the router for local or remote maintenance by using Telnet or SSH, you
can configure the corresponding VTY user interface as needed.
4.5 Configuration Examples
This section provides examples for configuring console, AUX, and VTY user interfaces. These
configuration examples explain networking requirements, configuration roadmap, and
configuration notes.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
35
Page 51
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.1 User Interface Overview
The system supports console, AUX, and VTY user interfaces.
Each user interface has a corresponding user interface view. A user interface view is a command
line view provided by the system. It is used to configure and manage all the physical and logical
interfaces in asynchronous mode.
User Interfaces Supported by the System
l Console port (CON)
The console port is a serial port provided by the main control board of the router.
The main control board provides one EIA/TIA-232 DCE console port for local
configuration by directly connecting a terminal to a router.
l Auxiliary port (AUX)
It is a linear port provided by the main control board of the router and supports the dialup
by using a modem.
Each main control board provides one AUX port with the type of EIA/TIA-232 DTE. A
terminal can remotely access the router through the modem on the AUX port.
l Virtual type terminal (VTY)
It is a logical terminal line. A VTY connection is set up when a router connects to a terminal
by means of Telnet. It is used for local or remote access to a router. A maximum of 16 users
can log in to the router by using the VTY user interface.
Numbering of a User Interface
After a user logs in to the router, the system assigns an idle user interface of the smallest number
to the user according to the user's login mode. You can number a user interface in the following
manners:
l Relative numbering
The relative numbering is in the format of user interface type + number.
The relative numbering is available for interfaces of a specific type. It is used only to specify
one or a group of user interfaces of a specified type. Relative numbering must comply with
the following rules:
– Number of the console port: CON 0
– Number of the auxiliary port: AUX 0
– Number of the VTY: VTY 0 for the first line, VTY 1 for the second line, and so on
l Absolute numbering
The absolute numbering is used to uniquely specify a user interface or a group of user
interfaces.
The number starts with 0. The ports are numbered in the sequence of CON → AUX →
VTY. There is only one console port and one AUX port and 0-15 VTY interfaces. You can
use the user-interface maximum-vty command to set the maximum number of user
interfaces. The default number is five.
By default, the system supports three types of user interfaces: CON, AUX, and VTY.
Table 4-1 shows the absolute numbers of the user interfaces in this system.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
36
Page 52
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Table 4-1 Example for the absolute numbering
Absolute number User-interface
0 CON0
33 AUX0
34 The first virtual interface (VTY0)
35 The second virtual interface (VTY1)
36 The third virtual interface (VTY2)
37 The fourth virtual interface (VTY3)
38 The fifth virtual interface (VTY4)
NOTE
The absolute numbers allocated for AUX and VTY interfaces are device-specific.
The numbers from 1 to 32 are reserved for the TTY user interfaces.
Run the display user-interface command to view the absolute number of user interfaces.
Authentication of a User Interface
After a user is configured, the system authenticates the user during user login.
There are three user authentication modes: non-authentication, password authentication, and
AAA.
l Non-authentication: In this mode, users can log in to the router without entering usernames
or passwords. For security, this mode is not recommended.
l Password authentication: In this mode, users need to enter passwords, not usernames,
during the login process.
l AAA authentication: In this mode, users need to enter passwords and usernames during the
login process. Telnet users are usually authenticated in this mode.
Priority of a User Interface
Users that log in to the router are managed according to their levels.
Similar to command levels, users are classified into 16 levels numbered 0 to 15. The greater the
number, the higher the user level.
The level of the command that a user can run is determined by the level of this user.
l In the case of non-authentication or password authentication, the level of the command that
the user can run is determined by the level of the user interface.
l In the case of AAA authentication, the command that the user can run is determined by the
level of the local user specified in the AAA configuration.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
37
Page 53
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.2 Configuring the Console User Interface
When a user logs in to the router by using a console port for local maintenance, you can configure
attributes for the corresponding console user interface are needed.
4.2.1 Establishing the Configuration Task
Before configuring the console user interface, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This can help
you complete the configuration task quickly and accurately.
Applicable Environment
If you need to log in to the router for local maintenance by using a console port, you can configure
the corresponding console user interface, including the physical attributes, terminal attributes,
user priority, and user authentication mode. The preceding parameters have default values on
the router and additional configuration is not needed. You can configure these parameters as
needed.
Pre-configuration Tasks
Before configuring a console user interface, complete the following tasks:
l Logging in to the router by using a terminal
Data Preparation
To configure a console user interface, you need the following data.
No.
1 Baud rate, flow-control mode, parity, stop bit, and data bit
2 Idle timeout period, number of lines displayed in a terminal screen, and the size of
3 User priority
4 User authentication method, user name, and password
Data
history command buffer
NOTE
All the default values (excluding the password and username) are stored on the router and do not need
additional configuration.
4.2.2 Setting Physical Attributes of Console User Interface
You can configure the rate, flow control mode, parity mode, stop bit, and data bit for the console
port.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
38
Page 54
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Context
Physical attributes of a console port have default values on the router and no additional
configuration is needed.
NOTE
When a user logs in to a router through a console port, the physical attributes set for the console port on
the HyperTerminal should be consistent with the attributes of the console user interface on the router.
Otherwise, the user cannot log in to the router.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface console interface-number
The console user interface view is displayed.
Step 3 Run:
speed speed-value
The baud rate is set.
By default, the baud rate is 9600 bit/s.
Step 4 Run:
flow-control { hardware | none | software }
The flow control mode is set. By default, the flow-control mode is none.
Step 5 Run:
parity { even | mark | none | odd | space }
The parity mode is set.
By default, the value is none.
Step 6 Run:
stopbits { 1.5 | 1 | 2 }
The stop bit is set.
By default, the value is 1 bit.
Step 7 Run:
databits { 5 | 6 | 7 | 8 }
The data bit is set.
By default, the data bit is 8.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
39
Page 55
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.2.3 Setting Terminal Attributes of Console User Interface
This section describes how to set terminal attributes of the console user interface, including the
user timeout disconnection function, number of lines displayed in a terminal screen, and size of
the history command buffer.
Context
Terminal attributes of the console user interface have default values on the router and you can
set them as needed.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface console interface-number
The console user interface view is displayed.
Step 3 Run:
shell
The terminal service is started.
Step 4 Run:
idle-timeout minutes [ seconds ]
The idle timeout period is set.
If the connection keeps idle within the timeout period, the system automatically terminates the
connection.
By default, the idle timeout period on the user interface is 10 minutes.
Step 5 Run:
screen-length screen-length [temporary]
The length of a terminal screen is set.
The parameter temporary is used to display the number of lines to be temporarily displayed on
a terminal screen.
By default, the length of a terminal screen is 24 lines.
Step 6 Run:
history-command max-size size-value
The history command buffer is set.
By default, the size of history command buffer on a user interface is 10 entries.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
40
Page 56
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.2.4 Configuring User Priority of Console User Interface
This section describes how to control users' authority of logging in to the router and improve
the security of managing the router by configuring the user priority.
Context
l Similar to command levels, users are classified into 16 levels numbered 0 to 15. The greater
the number, the higher the user level.
l This process is to set the priority for a user who logs in through the console port. A user
can only use the commands with the level corresponding to the user level.
For details about command levels, see "Command Level" in the chapter "CLI Overview" of
the Configuration Guide - Basic Configuration.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface console interface-number
The console user interface view is displayed.
Step 3 Run:
user privilege level level
The priority of the user is set.
NOTE
l By default, users logging in through the console user interface can use commands at level 3, and users
logging in through other user interfaces can use commands at level 0.
l If the command level is inconsistent with the user level, the user level takes precedence.
----End
4.2.5 Configuring the User Authentication Mode of the Console User Interface
The system provides three authentication modes: AAA, password authentication, and nonauthentication. Configuring the user authentication mode can improve the security of the
router.
Context
By default, the user authentication mode of the console user interface is non-authentication.
Procedure
l Configuring AAA Authentication
1. Run:
system-view
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
41
Page 57
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
The system view is displayed.
2. Run:
user-interface console interface-number
The console user interface view is displayed.
3. Run:
authentication-mode aaa
The authentication mode is set to AAA.
4. Run:
quit
Exit from the console user interface view.
5. Run:
aaa
The AAA view is displayed.
6. Run:
local-user user-name password { simple | cipher } password
Name and password of the local user are created.
l Configuring Password Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface console interface-number
The console user interface view is displayed.
3. Run:
authentication-mode password
You can set the authentication mode as password authentication.
4. Run:
set authentication password { cipher | simple } password
A password for authentication is set.
l Configuring Non-Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface console interface-number
The console user interface view is displayed.
3. Run:
authentication-mode none
The authentication mode is set to non-authentication.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
42
Page 58
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.2.6 Checking the Configuration
After configuring the console user interface, you can view information about the user interface,
physical attributes and configurations of the user interface, local user list, and online users.
Prerequisite
The configurations of the user management function are complete.
Procedure
l Run the display users [ all ] command to check information about the user interface.
l Run the display user-interface console ui-number1 [ summary ] command to check
physical attributes and configurations of the user interface.
l Run the display local-user command to check the local user list.
l Run the display access-user command to check the local user list.
----End
Example
Run the display users command, and you can view information about the current user interface.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
0 CON 0 00:00:44 pass no
Username : Unspecified
Run the display user-interface console ui-number1 [ summary ] command, and you can view
the physical attributes and configurations of the user interface.
<HUAWEI> display user-interface console 0
Idx Type Tx/Rx Modem Privi ActualPrivi Auth Int
0 CON 0 9600 - 3 - N -
+ : Current UI is active.
F : Current UI is active and work in async mode.
Idx : Absolute index of UIs.
Type : Type and relative index of UIs.
Privi: The privilege of UIs.
ActualPrivi: The actual privilege of user-interface.
Auth : The authentication mode of UIs.
A: Authenticate use AAA.
N: Current UI need not authentication.
P: Authenticate use current UI's password.
Int : The physical location of UIs.
Run the display local-user command, and you can view the local user list.
<HUAWEI> display local-user
--------------------------------------------------------------------------- Username State Type CAR Access-limit Online
--------------------------------------------------------------------------- user123 Active All Dft No 0
ll Active F Dft No 0
user1 Active F Dft No 0
--------------------------------------------------------------------------- Total 3,3 printed
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
43
Page 59
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.3 Configuring the AUX User Interface
When a user logs in to the router for local or remote configuration by using an AUX port,
configuring attributes in the corresponding AUX user interface is needed.
4.3.1 Establishing the Configuration Task
Before configuring the AUX user interface, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This can help
you complete the configuration task quickly and accurately.
Applicable Environment
If you need to log in to the router for remote maintenance by using an AUX port, you can
configure the corresponding AUX user interface as needed by setting the physical attributes,
terminal attributes, user priority, and user authentication mode. The preceding parameters have
default values on the router and additional configuration is not needed.
Pre-configuration Tasks
Before configuring an AUX user interface, complete the following tasks:
l Logging in to the router by using a terminal
Data Preparation
Before configuring an AUX user interface, you need the following data.
No.
1 Baud rate, flow-control mode, parity, stop bit, and data bit
2 Idle timeout period, number of lines displayed in a terminal screen, and the size of
3 User priority
4 Modem attributes
5 (Optional) Auto-execute commands
6 User authentication method, user name, and password
Data
history command buffer
NOTE
All the default values (excluding the auto-run commands, password, and username) are stored on the
router and do not need additional configuration.
4.3.2 Setting Physical Attributes of AUX User Interface
Physical attributes of the AUX user interface include the transmission rate, flow control mode,
parity mode, stop bit, and data bit of the AUX port.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
44
Page 60
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Context
Physical attributes of the AUX user interface have default values on the router and no additional
configuration is needed.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface aux interface-number
The AUX user interface view is displayed.
Step 3 Run:
speed speed-value
The transmission rate is set.
By default, the baud rate is 9600 bit/s.
Step 4 Run:
flow-control { hardware | none | software }
The flow control mode is set.
By default, the flow-control mode is none.
Step 5 Run:
parity { even | mark | none | odd | space }
The parity mode is set.
By default, the value is none.
Step 6 Run:
stopbits { 1.5 | 1 | 2 }
The stop bit is set.
By default, the value is 1 bit.
Step 7 Run:
databits { 5 | 6 | 7 | 8 }
The data bit is set.
By default, the value is 8.
NOTE
When the user logs in to a router through an AUX port, the configured attributes for the console port on
the HyperTerminal should be in accordance with the attributes of the AUX user interface on the router.
Otherwise, the user cannot log in to the router.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
45
Page 61
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.3.3 Setting Terminal Attributes of AUX User Interface
This section describes how to configure terminal attributes of the AUX user interface, including
the user idle timeout, number of lines displayed in a terminal screen, and size of the history
command buffer.
Context
Terminal attributes of the AUX user interface have default values on the router and you can
configure them as needed.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface aux interface-number
The AUX user interface view is displayed.
Step 3 Run:
shell
AUX terminal service is enabled.
Step 4 Run:
idle-timeout minutes [ seconds ]
User idle timeout is enabled.
If the connection keeps idle within the timeout period, the system automatically terminates the
connection.
By default, idle timeout period on the interface is 10 minutes.
Step 5 Run:
screen-length screen-length [temporary]
The length of a terminal screen is set.
The parameter temporary is used to display the number of lines to be temporarily displayed on
a terminal screen.
By default, the length of a terminal screen is 24 lines.
Step 6 Run:
history-command max-size size-value
The size of the history command buffer is configured.
By default, the size of history command buffer on user interface is 10 entries.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
46
Page 62
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
4.3.4 Setting User Priority of AUX User Interface
This section describes how to control users' authority of logging in to the router and improve
the security of managing the router by configuring the user priority.
Context
l Similar to command levels, users are classified into 16 levels numbered 0 to 15. The greater
the number, the higher the user level.
l This process is to set the priority for a user who logs in through the console port. A user
can only use the commands with the level corresponding to the user level.
For details about command levels, see "Command Level" in the chapter "CLI Overview" of
the Configuration Guide - Basic Configuration.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface aux interface-number
The AUX user interface view is displayed.
Step 3 Run:
user privilege level level
The user priority is set.
NOTE
l By default, users logging in by using the AUX user interface can use commands at level 0.
l If the authority to use commands is inconsistent with the user level, the user level takes precedence.
----End
4.3.5 Setting Modem Attributes of AUX User Interface
You can set the time period from picking up the signal to detecting the carrier when a call is
established, modem for only incoming calls or for both incoming and outgoing calls, and
automatic answer.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface aux interface-number
The AUX user interface view is displayed.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
47
Page 63
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Step 3 Run:
modem timer answer seconds
The period between the system receiving the ring signal and the system waiting for the CD_UP
is set. That is the time that elapses between picking up the signal to detecting the carrier, since
the call is established.
By default, the waiting time is 30 seconds.
Step 4 Run:
modem [ both | call-in ]
The switch of incoming call or outgoing call is set.
By default, incoming and outgoing calls are prohibited.
Step 5 Run:
modem auto-answer
Automatic answer is enabled.
By default, manual answering is enabled.
----End
4.3.6 (Optional) Configuring Auto-Execute Commands of AUX User Interface
You can set a command to be an auto-executed command.
Context
CAUTION
After the auto-execute command command is run, you cannot perform general configuration
in the system through a terminal.
Before configuring the auto-execute command command and the save command to save the
existing configurations, ensure that you can log in to the system using other methods to delete
the configurations.
Do as follows on the router that the user logs in to:
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface aux 0
The AUX user interface view is displayed.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
48
Page 64
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Step 3 Run:
auto-execute command command
A command is specified as an auto-execute command.
Generally, the auto-execute command command is run to configure Telnet on a terminal. After
the configuration, the user can automatically connect to a designated host.
----End
4.3.7 Setting User Authentication Mode of AUX User Interface
The system provides three authentication modes: AAA, password authentication, and nonauthentication. Configuring the user authentication mode can improve the security of the
router.
Context
By default, the user authentication mode of the AUX user interface is non-authentication.
Procedure
l Configuring AAA Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface aux interface-number
The AUX user interface view is displayed.
3. Run:
authentication-mode aaa
The authentication mode is set to AAA.
4. Run:
quit
Exit from the AUX user interface view.
5. Run:
aaa
The AAA view is displayed.
6. Run:
local-user user-name password { simple | cipher } password
Local user and password are configured.
l Configuring Password Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface aux interface-number
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
49
Page 65
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
The AUX user interface view is displayed.
3. Run:
authentication-mode password
The authentication mode is set to password.
4. Run:
set authentication password { cipher | simple } password
A password is set.
l Configuring Non-Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface aux interface-number
The AUX user interface view is displayed.
3. Run:
authentication-mode none
The authentication mode is set to non-authentication.
----End
4.3.8 Checking the Configuration
After configuring the AUX user interface, you can view the usage information of the user
interface, physical attributes and configurations of the user interface, local user list, and online
users.
Prerequisite
Configurations of the AUX user interface are complete.
Procedure
l Run the display users [ all ] command to check usage information about the AUX user
interface.
l Run the display user-interface aux interface-number [ summary ] command to check
physical attributes and configurations of the user interface.
l Run the display local-user command to check the local user list.
l Run the display access-user command to check the local user list.
----End
Example
Run the display users command, and you can view information about the current user interface.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
33 AUX 0 00:00:44 pass no
Username : Unspecified
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
50
Page 66
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Run the display user-interface aux ui-number1 [ summary ] command, and you can view the
physical attributes and configurations of the user interface.
<HUAWEI> display user-interface aux 0
Idx Type Tx/Rx Modem Privi ActualPrivi Auth Int
33 AUX 0 9600 - 0 - N -
+ : Current UI is active.
F : Current UI is active and work in async mode.
Idx : Absolute index of UIs.
Type : Type and relative index of UIs.
Privi: The privilege of UIs.
ActualPrivi: The actual privilege of user-interface.
Auth : The authentication mode of UIs.
A: Authenticate use AAA.
N: Current UI need not authentication.
P: Authenticate use current UI's password.
Int : The physical location of UIs.
Run the display local-user command, and you can view the local user list.
<HUAWEI> display local-user
--------------------------------------------------------------------------- Username State Type CAR Access-limit Online
--------------------------------------------------------------------------- user123 Active All Dft No 0
ll Active F Dft No 0
user1 Active F Dft No 0
--------------------------------------------------------------------------- Total 3,3 printed
4.4 Configuring VTY User Interface
If you need to log in to the router for local or remote maintenance by using Telnet or SSH, you
can configure the corresponding VTY user interface as needed.
4.4.1 Establishing the Configuration Task
Before configuring the VTY user interface, familiarize yourself with the applicable environment,
complete the pre-configuration tasks, and obtain the required data. This can help you complete
the configuration task quickly and accurately.
Applicable Environment
If you need to log in to the router for local or remote maintenance by using Telnet or SSH, you
can configure the corresponding VTY user interface, including the maximum number of VTY
user interfaces, limit of incoming and outgoing calls, user priority, and user authentication mode.
The preceding parameters have default values on the router. You can also set these parameters
as needed.
Pre-configuration Tasks
Before configuring VTY user interface, complete the following tasks:
l Logging in to the router by using a terminal
Data Preparation
To configure a VTY user interface, you need the following data.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
51
Page 67
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
No. Data
1 Maximum VTY user interfaces
2 (Optional) ACL code to limit VTY user interface to call in and out
3 Idle timeout period, number of characters in each line displayed in a terminal screen
4 User priority
5 User authentication method, user name, and password
NOTE
All the preceding parameters (excluding the ACL for limiting incoming and outgoing calls in VTY user
interfaces, password, and user name) have default values on the router, and no additional configuration is
needed.
4.4.2 Configuring Maximum VTY User Interfaces
Context
Procedure
Step 1 Run:
Step 2 Run:
This section describes how to limit the number of users logging in to the router by configuring
the maximum number of VTY user interfaces.
The maximum number of VTY user interfaces is the total number of users logging in to the
router by using Telnet and SSH.
system-view
The system view is displayed.
user-interface maximum-vty number
The maximum VTY user interfaces that can log in to the router is set.
NOTE
When the maximum number of VTY user interfaces is set to zero, any user (including the NMS user) cannot
log in to the router by using a VTY user interface.
If the maximum number of VTY user interfaces to be configured is smaller than the maximum
number of current interfaces, current online users will not be affected and no addition
configuration is needed.
If the maximum number of VTY user interfaces to be configured is larger than the maximum
number of current interfaces, the authentication mode and password need to be configured for
newly added user interfaces.
For newly added user interfaces, the system defaults to password authentication.
For example, a maximum of five users are allowed online. To allow 15 VTY users online at the
same time, you need to run the authentication-mode command and the set authentication
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
52
Page 68
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
password command to configure authentication modes and passwords for user interfaces from
VTY 5 to VTY 14. The command is run as follows:
<HUAWEI> system-view
[HUAWEI] user-interface maximum-vty 15
[HUAWEI] user-interface vty 5 14
[HUAWEI-ui-vty5-14] authentication-mode password
[HUAWEI-ui-vty5-14] set authentication password cipher huawei
----End
4.4.3 (Optional)Setting Limit on Incoming and Outgoing Calls of VTY User Interfaces
This section describes how to configure an ACL to limit incoming and outgoing calls of the
VTY user interface.
Context
Before setting the limit on incoming and outgoing calls of the VTY user interface, run the acl
command in the system view to create an ACL and enter the ACL view. Then, run the rule
command to add rules to the ACL.
Procedure
Step 1 Run:
Step 2 Run:
Step 3 Run:
NOTE
The user interface supports the basic ACL ranging from 2000 to 2999 and the advanced ACL ranging from
3000 to 3999.
system-view
The system view is displayed.
user-interface vty first-ui-number [ last-ui-number ]
The VTY user interface view is displayed.
acl acl-number { inbound | outbound }
The limits to calling in/out of VTY are configured.
l When you need to prevent a user of certain address or segment address from logging in to
the router, use the inbound command.
l When you need to prevent a user who logs in to a router from accessing other routers, use
the outbound command.
----End
4.4.4 Setting Terminal Attributes of the VTY User Interface
This section describes how to configure terminal attributes of the VTY user interface, including
user idle timeout, number of lines displayed in a terminal screen, and size of the history command
buffer.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
53
Page 69
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Context
Terminal attributes of the VTY user interface have default values on the router and you can set
them as needed.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface vty number1 [ number2 ]
The VTY user interface view is displayed.
Step 3 Run:
shell
VTY terminal service is enabled.
Step 4 Run:
idle-timeout minutes [ seconds ]
User idle timeout is enabled.
If the connection keeps idle within the timeout period, the system automatically terminates the
connection.
By default, the timeout period is 10 minutes.
Step 5 Run:
screen-length screen-length [temporary]
The length of a terminal screen is set.
The parameter temporary is used to display the number of lines to be temporarily displayed on
a terminal screen.
By default, the length of a terminal screen is 24 lines.
Step 6 Run:
history-command max-size size-value
Set the size of the history command buffer.
By default, a maximum number of 10 commands can be cached in the history command buffer.
----End
4.4.5 Setting User Priority of VTY User Interface
This section describes how to control users' authority of logging in to the router and improve
the security of managing the router by configuring the user priority.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
54
Page 70
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Context
l Similar to command levels, users are classified into 16 levels numbered 0 to 15. The greater
the number, the higher the user level.
l This process is to set the priority for a user who logs in through the console port. A user
can only use the commands with the level corresponding to the user level.
For details about command levels, see "Command Level" in the chapter "CLI Overview" of
the Configuration Guide - Basic Configuration.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface vty interface-number
The VTY user interface view is displayed.
Step 3 Run:
user privilege level level
The user priority is set.
By default, users logging in through the VTY user interface can use commands at level 0.
NOTE
If the command level configured in the VTY user interface view is inconsistent with the user priority, the
user priority takes effect.
----End
4.4.6 Setting User Authentication Mode of the VTY User Interface
The system provides three authentication modes: AAA, password authentication, and nonauthentication. Configuring the user authentication mode can improve the security of the
router.
Context
By default, the user authentication mode of the VTY user interface is password authentication.
Procedure
l Configuring AAA Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface vty number1 [ number2 ]
The VTY user interface view is displayed.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
55
Page 71
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
3. Run:
authentication-mode aaa
The authentication mode is set to AAA.
4. Run:
quit
Exit from the VTY user interface view.
5. Run:
aaa
The AAA view is displayed.
6. Run:
local-user user-name password { simple | cipher } password
Name and password of the local user are created.
l Configuring Password Authentication
1. Run:
system-view
The system view is displayed.
2. Run:
user-interface vty number1 [ number2 ]
The VTY user interface view is displayed.
3. Run:
authentication-mode password
Set the authentication mode as password.
4. Run:
set authentication password { cipher | simple } password
A password for this authentication mode is set.
l Configuring Non-Authentication
1. Do as follows on the router, run:
system-view
The system view is displayed.
2. Run:
user-interface vty number1 [ number2 ]
The VTY user interface view is displayed.
3. Run:
authentication-mode none
The authentication mode is set to none.
----End
4.4.7 (Optional) Configuring NMS Users to Log In Through VTY User Interfaces
Network Management System (NMS) users can log in to a device through VTY user interfaces
to set parameters about the device.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
56
Page 72
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Context
NMS users can log in to the router through VTY user interfaces to set parameters about the
router.
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
aaa
The AAA view is displayed.
Step 3 Run:
local-user user-name password { simple | cipher } password
A local user is created.
Step 4 Run:
local-user user-name user-type netmanager
The local user is set as an NM user.
Step 5 Run:
quit
The system view is displayed.
Step 6 Run:
user-interface vty first-ui-number [ last-ui-number ]
The user interface view is displayed.
Step 7 Run:
authentication-mode aaa
An authentication mode used to log in to the user interface is configured.
NOTE
The system reserves five VTYs (VTY 16-VTY 20) for an NMS user. The five VTYs are used as special
channels of the network management. The channels do not support the RSA authentication mode but
support the password authentication.
Step 8 Run:
quit
The system view is displayed.
Step 9 Run:
mmi-mode enable
The system is switched to the machine-to-machine mode.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
57
Page 73
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
NOTE
l This command is invisible to terminals and cannot be obtained by using the online help. In man-to-
machine mode, exercise caution when using this command.
l In the VTY machine-to-machine mode, the system reserves five user interfaces to which an NMS user
can log in through VTYs. A common user cannot log in through Telnet but can log in by using the five
reserved user interfaces.
l In the machine-to-machine mode, the system does not output logs, alarms, and debugging information
to the screen.
l In the machine-to-machine mode, the save and reboot commands can be used directly.
l In the machine-to-machine mode, a maximum of 512 lines are displayed by default. The value can be
adjusted by using the screen-length command. In addition, you can run the screen-length
temporary command to adjust the number of lines temporarily displayed on the screen.
----End
4.4.8 Checking the Configuration
After configuring the VTY user interface, you can view information about user interfaces, the
maximum number of VTY user interfaces, and physical attributes and configurations of user
interfaces.
Prerequisite
Procedure
Example
The configurations of the VTY user interface are complete.
l Run the display users [ all ] command to check information about user interfaces.
l Run the display user-interface maximum-vty command to check the maximum number
of VTY user interfaces.
l Run the display user-interface [ [ ui-type ] ui-number1 | ui-number ] [ summary ]
command to check the physical attributes and configurations of user interfaces.
l Run the display local-user command to check the local user list.
l Run the display vty mode command to check the VTY mode.
----End
Run the display users command, and you can view information about the current user interfaces.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
34 VTY 0 00:00:12 TEL 10.138.77.38 no
Username : Unspecified
+ 35 VTY 1 00:00:00 TEL 10.138.77.57 no
Username : Unspecified
Run the display user-interface maximum-vty command, and you can view the maximum
number of VTY user interfaces.
<HUAWEI> display user-interface maximum-vty
Maximum of VTY user:15
Run the display user-interface vty [ ui-number1 | ui-number ] [ summary ] command to check
the physical attributes and configurations of user interfaces.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
58
Page 74
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
<HUAWEI> display user-interface vty 0
Idx Type Tx/Rx Modem Privi ActualPrivi Auth Int
+ 34 VTY 0 - 14 14 N + : Current UI is active.
F : Current UI is active and work in async mode.
Idx : Absolute index of UIs.
Type : Type and relative index of UIs.
Privi: The privilege of UIs.
ActualPrivi: The actual privilege of user-interface.
Auth : The authentication mode of UIs.
A: Authenticate use AAA.
N: Current UI need not authentication.
P: Authenticate use current UI's password.
Int : The physical location of UIs.
Run the display local-user command, and you can view the local user list.
<HUAWEI> display local-user
--------------------------------------------------------------------------- Username State Type CAR Access-limit Online
--------------------------------------------------------------------------- user123 Active All Dft No 0
ll Active F Dft No 0
user1 Active F Dft No 0
--------------------------------------------------------------------------- Total 3,3 printed
Run the display vty mode command, and you can view the prompt message indicating that the
machine-to-machine interface is enabled. For example:
<HUAWEI> display vty mode
current VTY mode is Machine-Machine interface
4.5 Configuration Examples
This section provides examples for configuring console, AUX, and VTY user interfaces. These
configuration examples explain networking requirements, configuration roadmap, and
configuration notes.
4.5.1 Example for Configuring Console User Interface
This part provides an example describing how to configure the console user interface. In this
configuration example, to allow a user in password authentication mode to log in to the router
by using a console user interface, multiple attributes of the console user interface are set,
including physical attributes, terminal attributes, user priority, user authentication mode, and
password.
Networking Requirements
To initialize configurations of the router or locally maintain the router, a user can log in to the
router through a console user interface. To allow the user to log in, you can set attributes of the
console user interface as needed (for security reasons, for example).
In the console user interface view, the user priority is set to 15, and the password authentication
mode is set (the password is huawei).
After a user logs in, if the user takes no action on the router for more than 30 minutes, the
connection between the user and the router is torn down.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
59
Page 75
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Configuration Roadmap
The configuration roadmap is as follows:
1. Enter the interface view and set physical attributes of the console user interface.
2. Set terminal attributes of the console user interface.
3. Set the user priority of the console user interface.
4. Set the user authentication mode and password of the console user interface.
Data Preparation
To complete the configuration, you need the following data:
l Transmission rate of the console user interface: 4800 bit/s
l Flow control mode of the console user interface: None
l Parity of the console user interface: even
l Stop bit of the console user interface: 2
l Data bit of the console user interface: 6
l Timeout period for disconnecting from the console user interface: 30 minutes
l Number of lines that a terminal screen displays: 30
l Size of the history command buffer: 20
l User priority: 15
l User authentication mode: password (password: huawei)
Procedure
Step 1 Set physical attributes of the console user interface.
Step 2 Set terminal attributes of the console user interface.
Step 3 Set the user priority of the console user interface.
Step 4 Set the user authentication mode in the console user interface to password.
<HUAWEI> system-view
[HUAWEI] user-interface console 0
[HUAWEI-ui-console0] speed 4800
[HUAWEI-ui-console0] flow-control none
[HUAWEI-ui-console0] parity even
[HUAWEI-ui-console0] stopbits 2
[HUAWEI-ui-console0] databits 6
[HUAWEI-ui-console0] shell
[HUAWEI-ui-console0] idle-timeout 30
[HUAWEI-ui-console0] screen-length 30
[HUAWEI-ui-console0] history-command max-size 20
[HUAWEI-ui-console0] user privilege level 15
[HUAWEI-ui-console0] authentication-mode password
[HUAWEI-ui-console0] set authentication password simple huawei
[HUAWEI-ui-console0] quit
After the console user interface is configured, a user in password authentication mode can log
in to the router through a console port, implementing local maintenance of the router. For details
on how a user logs in to the router, see the 5 Configuring User Login.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
60
Page 76
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
Configuration Files
#
sysname HUAWEI
#
user-interface con 0
authentication-mode password
user privilege level 15
set authentication password simple huawei
history-command max-size 20
idle-timeout 30 0
screen-length 30
databits 6
parity even
stopbits 2
speed 4800
screen-length 30
#
return
4.5.2 Example for Configuring AUX User Interface
This part provides an example describing how to configure the AUX user interface. In the
configuration example, to allow a user in AAA authentication mode to log in to the router by
using an AUX user interface, multiple attributes of the console user interface are set, including
physical attributes, terminal attributes, user priority, user authentication mode, and password.
Networking Requirements
To maintain the router locally or remotely, a user can log in to the router through an AUX user
interface.
To allow the user login, an operator can set attributes of the AUX user interface as needed (for
security reasons, for example).
In the AUX user interface, the user priority is set to 15, and the authentication mode is set to
AAA, with the user name of user123 and the password of huawei.
After a user logs in, if the user takes no action on the router for more than 30 minutes, the
connection between the user and the router is torn down.
Configuration Roadmap
The configuration roadmap is as follows:
1. Enter the interface view and set physical attributes of the AUX user interface.
2. Set terminal attributes of the AUX user interface.
3. Set the user priority of the AUX user interface.
4. Set modem attributes of the AUX user interface.
5. Set the authentication mode and password in the AUX user interface.
Data Preparation
To complete the configuration, you need the following data:
l Transmission rate of the AUX user interface: 9600 bit/s
l Flow control mode of the AUX user interface: None
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
61
Page 77
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
l Parity of the AUX user interface: None
l Stop bit of the AUX user interface: 1
l Data bit of the AUX user interface: 8
l Timeout period for disconnecting from the AUX user interface: 30 minutes
l Number of lines that a terminal screen displays: 30
l Size of the history command buffer: 20
l User priority: 15
l Modem attributes: idle timeout from off-hook to carrier detection (45 seconds), call-in
permission, and automatic response
l User authentication mode and password in the AUX user interface
Procedure
Step 1 Set physical attributes of the AUX user interface.
<HUAWEI> system-view
[HUAWEI] user-interface aux 0
[HUAWEI-ui-aux0] speed 9600
[HUAWEI-ui-aux0] flow-control none
[HUAWEI-ui-aux0] parity none
[HUAWEI-ui-aux0] stopbits 1
[HUAWEI-ui-aux0] databits 8
All the preceding physical attributes of the AUX user interface are set with default values. In
fact, if a user chooses to use the default values, the user does not need to set them. The preceding
settings only mean to provide the configuration method.
Step 2 Set terminal attributes of the AUX user interface.
[HUAWEI-ui-aux0] shell
[HUAWEI-ui-aux0] idle-timeout 30
[HUAWEI-ui-aux0] screen-length 30
[HUAWEI-ui-aux0] history-command max-size 20
Step 3 Set the user priority of the AUX user interface.
[HUAWEI-ui-aux0] user privilege level 15
Step 4 Set modem attributes of the AUX user interface.
[HUAWEI-ui-aux0] modem timer answer 45
[HUAWEI-ui-aux0] modem call-in
[HUAWEI-ui-aux0] modem auto-answer
Step 5 Set the authentication mode of the AUX user interface to AAA.
[HUAWEI-ui-aux0] authentication-mode aaa
[HUAWEI-ui-aux0] quit
[HUAWEI] aaa
[HUAWEI-aaa] local-user user123 password simple huawei
[HUAWEI-aaa] quit
After the AUX user interface is configured, a user in AAA authentication mode can log in to
the router through an AUX port, implementing maintenance of the router. For details on how a
user logs in to the router, refer to the 5 Configuring User Login.
----End
Configuration Files
#
sysname HUAWEI
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
62
Page 78
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
#
user-interface aux 0
authentication-mode aaa
user privilege level 15
history-command max-size 20
idle-timeout 30 0
modem call-in
modem auto-answer
modem timer answer 45
screen-length 30
#
return
4.5.3 Example for Configuring VTY User Interface
This part provides an example describing how to configure the VTY user interface. In this
configuration example, to allow a user in password authentication mode to log in to the router
by using Telnet or SSH (Stelnet), multiple attributes of the VTY user interface are set, including
the maximum number of VTY user interfaces, call-in and call-out limit, terminal attributes,
authentication mode, and password.
Networking Requirements
A user logs in to the router through a VTY channel by using Telnet or SSH. To allow the user
login, an operator can set attributes of the VTY user interface as needed (for security reasons,
for example).
In the VTY user interface, the user priority is set to 15, the authentication mode is set to password,
with the password of "huawei", and the user with the IP address of 10.1.1.1 is prohibitted from
logging in to the router.
After logging in, if the user takes no action on the router for more than 30 minutes, the connection
between the user and the router is torn down.
Configuration Roadmap
The configuration roadmap is as follows:
1. Enter the interface view and set the maximum number of VTY user interfaces to 15.
2. Set the call-in and call-out limit of the VTY user interface, limiting the access of an IP
address or an IP address segment to the router.
3. Set terminal attributes of the VTY user interface.
4. Set the user priority in the VTY user interface.
5. Set the authentication mode and password in the VTY user interface.
Data Preparation
To complete the configuration, you need the following data:
l Maximum number of VTY user interfaces: 15
l ACL applied to limit call-in in the VTY user interface: 2000
l Timeout period for disconnecting from the VTY user interface: 30 minutes
l Number of lines that a terminal screen displays: 30
l Size of the history command buffer: 20
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
63
Page 79
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 4 Configuring User Interface
l User priority: 15
l User authentication mode: password, password: huawei
Procedure
Step 1 Set the maximum number of VTY user interfaces.
<HUAWEI> system-view
[HUAWEI] user-interface maximum-vty 15
Step 2 Set the limit on call-in and call-out in the VTY user interface.
[HUAWEI] acl 2000
[HUAWEI-acl-basic-2000] rule deny source 10.1.1.1 0
[HUAWEI-acl-basic-2000] quit
[HUAWEI] user-interface vty 0 14
[HUAWEI-ui-vty0-14] acl 2000 inbound
Step 3 Set terminal attributes of the VTY user interface.
[HUAWEI-ui-vty0-14] shell
[HUAWEI-ui-vty0-14] idle-timeout 30
[HUAWEI-ui-vty0-14] screen-length 30
[HUAWEI-ui-vty0-14] history-command max-size 20
Step 4 Set the user priority in the VTY user interface.
[HUAWEI-ui-vty0-14] user privilege level 15
Step 5 Set the authentication mode and password in the VTY user interface.
[HUAWEI-ui-vty0-14] authentication-mode password
[HUAWEI-ui-vty0-14] set authentication password simple huawei
[HUAWEI-ui-vty0-14] quit
After the VTY user interface is configured, a user authenticated in password mode can log in to
the router by using Telnet or SSH (Stelnet), implementing local or remote maintenance of the
router. For details on how a user logs in to the router, see the 5 Configuring User Login.
----End
Configuration Files
#
sysname HUAWEI
#
acl number 2000
rule 5 deny source 10.1.1.1 0
rule permit source any
#
user-interface maximum-vty 15
user-interface vty 0 14
acl 2000 inbound
user privilege level 15
set authentication password simple huawei
history-command max-size 20
idle-timeout 30 0
screen-length 30
#
return
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
64
Page 80
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5 Configuring User Login
About This Chapter
A user can log in to the router through a console port, an AUX port, or by using Telnet or SSH
(STelnet). After the login, the user can maintain the router locally or remotely.
5.1 Overview of User Login
Users can manage and maintain the router only after logging in to the router. Users can log in
to the router by using the AUX port, console port, Telnet, or STelnet (SSH Telnet).
5.2 Logging in to the Devices Through the Console Port
When a user needs to configure the router that is powered on for the first time or locally maintain
the router, the user can log in to the router through a console port.
5.3 Logging in to the Devices Through the AUX Port
When a user terminal and the router have no reachable route between each other, the user can
remotely configure and manage or locally maintain the router by logging in to the router through
an AUX port.
5.4 Logging in to the Devices by Using Telnet
If multiple routers need to be configured and managed, you do not need to connect the routers
and maintain them locally one by one. Instead, you can log in to the routers from a terminal by
using Telnet. This implements remote maintenance of the router and greatly facilitates device
management.
5.5 Logging in to the Devices by Using STelnet
STelnet provides secured remote access over an insecure network. After the client/server
negotiation is complete and a secured connection is established, a user can log in to the router
in a similar way as Telnet.
5.6 Common Operations After Login
After logging in to the router, you can perform following operations as needed, such as user
priority switching and terminal window locking.
5.7 Configuration Examples
This section provides several examples describing how to configure user login by using a console
port, Telnet, or STelnet. You can understand the configuration procedures by referring to the
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
65
Page 81
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
configuration flowchart. The configuration examples provide information about the networking
requirements, configuration notes, and configuration roadmap.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
66
Page 82
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5.1 Overview of User Login
Users can manage and maintain the router only after logging in to the router. Users can log in
to the router by using the AUX port, console port, Telnet, or STelnet (SSH Telnet).
To configure, monitor, and maintain the local or remote network devices running NE80E/40E,
you need to configure the user interface, the user management, and the terminal service.
The user interface provides a login plane. The user management guarantees the login security
and the terminal service provides related processes of login protocol.
The NE80E/40E supports the following login methods:
l Login through the console port
l Local or remote login through the AUX port
l Local or remote login through Telnet or STelnet
Table 5-1 User login modes
Login Mode Application
Console port Users log in to the router through the console port to configure the router
locally. Login through the console port is required when the router is
powered on for the first time.
Telnet Users log in to the router by using Telnet for local and remote maintenance.
Telnet helps users maintain remote devices but brings security threats.
AUX port Users log in to the router through the AUX port to maintain the router locally
when there is no available route and Telnet is unsuitable.
SSH (STelnet) SSH (STelnet) provides security protection for users logging in to the
router to maintain the router locally or remotely.
NOTE
Logins by using Telnet bring security risks because no secure authentication mechanism is available and
data is transmitted by using TCP in plain text mode. Unlike Telnet, SSH guarantees secure data transmission
on a conventional insecure network by authenticating the client and encrypting data in both directions. SSH
supports security Telnet (STelnet).
For detailed information about SSH, see the NE80E/40E Feature Description - Basic Configurations.
5.2 Logging in to the Devices Through the Console Port
When a user needs to configure the router that is powered on for the first time or locally maintain
the router, the user can log in to the router through a console port.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
67
Page 83
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5.2.1 Establishing the Configuration Task
Before configuring user login through a console port, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This will help
you complete the configuration task quickly and accurately.
Applicable Environment
A user can log in to the router locally through a console port. If the router is powered on for the
first time, the user has to log in through a console port.
Pre-configuration Tasks
Before configuring user login through a console port, complete the following tasks:
l Configuring the PC/terminal (including the serial port and RS-232 cable)
l Installing the terminal emulator (such as HyperTerminal of Windows XP) to the PC
Data Preparation
To configure user login through a console port, you need the following data.
No. Data
1
l Transmission rate, flow control mode, parity mode, stop bit, data bit
l Number of lines displayed in a terminal screen, size of the history command buffer
l User priority
l User authentication mode, user name, and password
5.2.2 Configuring Console User Interface
To allow users to log in to the router through a console port, configure attributes of the console
user interface.
Context
Attributes of an console user interface have default values on the router, and generally need no
additional settings. To meet specific application requirements or ensure network security, you
can set attributes of the console user interface, such as terminal attributes and user authentication
mode.
For detailed settings, see Configuring Console User Interface.
5.2.3 Logging in to the router Through a Console Port
A user can log in to the router by connecting a terminal with the router through a console port.
Context
For details, see Login Through the Console Portrouter.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
68
Page 84
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
NOTE
l Communication parameters of the user terminal must be consistent with the physical attribute
parameters of the console user interface on the router.
l If a user authentication mode is specified in the console user interface, a user can log in to the router
only after passing the authentication. This enhances network security.
5.2.4 Checking the Configuration
After a user logs in through a console port, the user can view information on the console user
interface, such as use information, physical attributes and configurations, local user list, and
online users.
Prerequisite
Configurations of user login through a console port are complete.
Procedure
l Run the display users [ all ] command to check information about the user interface.
l Run the display user-interface console ui-number1 [ summary ] command to check
physical attributes and configurations of the user interface.
l Run the display local-user command to check the local user list.
l Run the display access-user command to check the local user list.
Example
----End
Run the display users command, and you can view information about the current user interface.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
0 CON 0 00:00:44 pass no
Username : Unspecified
Run the display user-interface console ui-number1 [ summary ] command, and you can view
the physical attributes and configurations of the user interface.
<HUAWEI> display user-interface console 0
Idx Type Tx/Rx Modem Privi ActualPrivi Auth Int
0 CON 0 9600 - 3 - N -
+ : Current UI is active.
F : Current UI is active and work in async mode.
Idx : Absolute index of UIs.
Type : Type and relative index of UIs.
Privi: The privilege of UIs.
ActualPrivi: The actual privilege of user-interface.
Auth : The authentication mode of UIs.
A: Authenticate use AAA.
N: Current UI need not authentication.
P: Authenticate use current UI's password.
Int : The physical location of UIs.
Run the display local-user command, and you can view the local user list.
<HUAWEI> display local-user
----------------------------------------------------------------------------
Username State Type CAR Access-limit Online
----------------------------------------------------------------------------
user123 Active All Dft No 0
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
69
Page 85
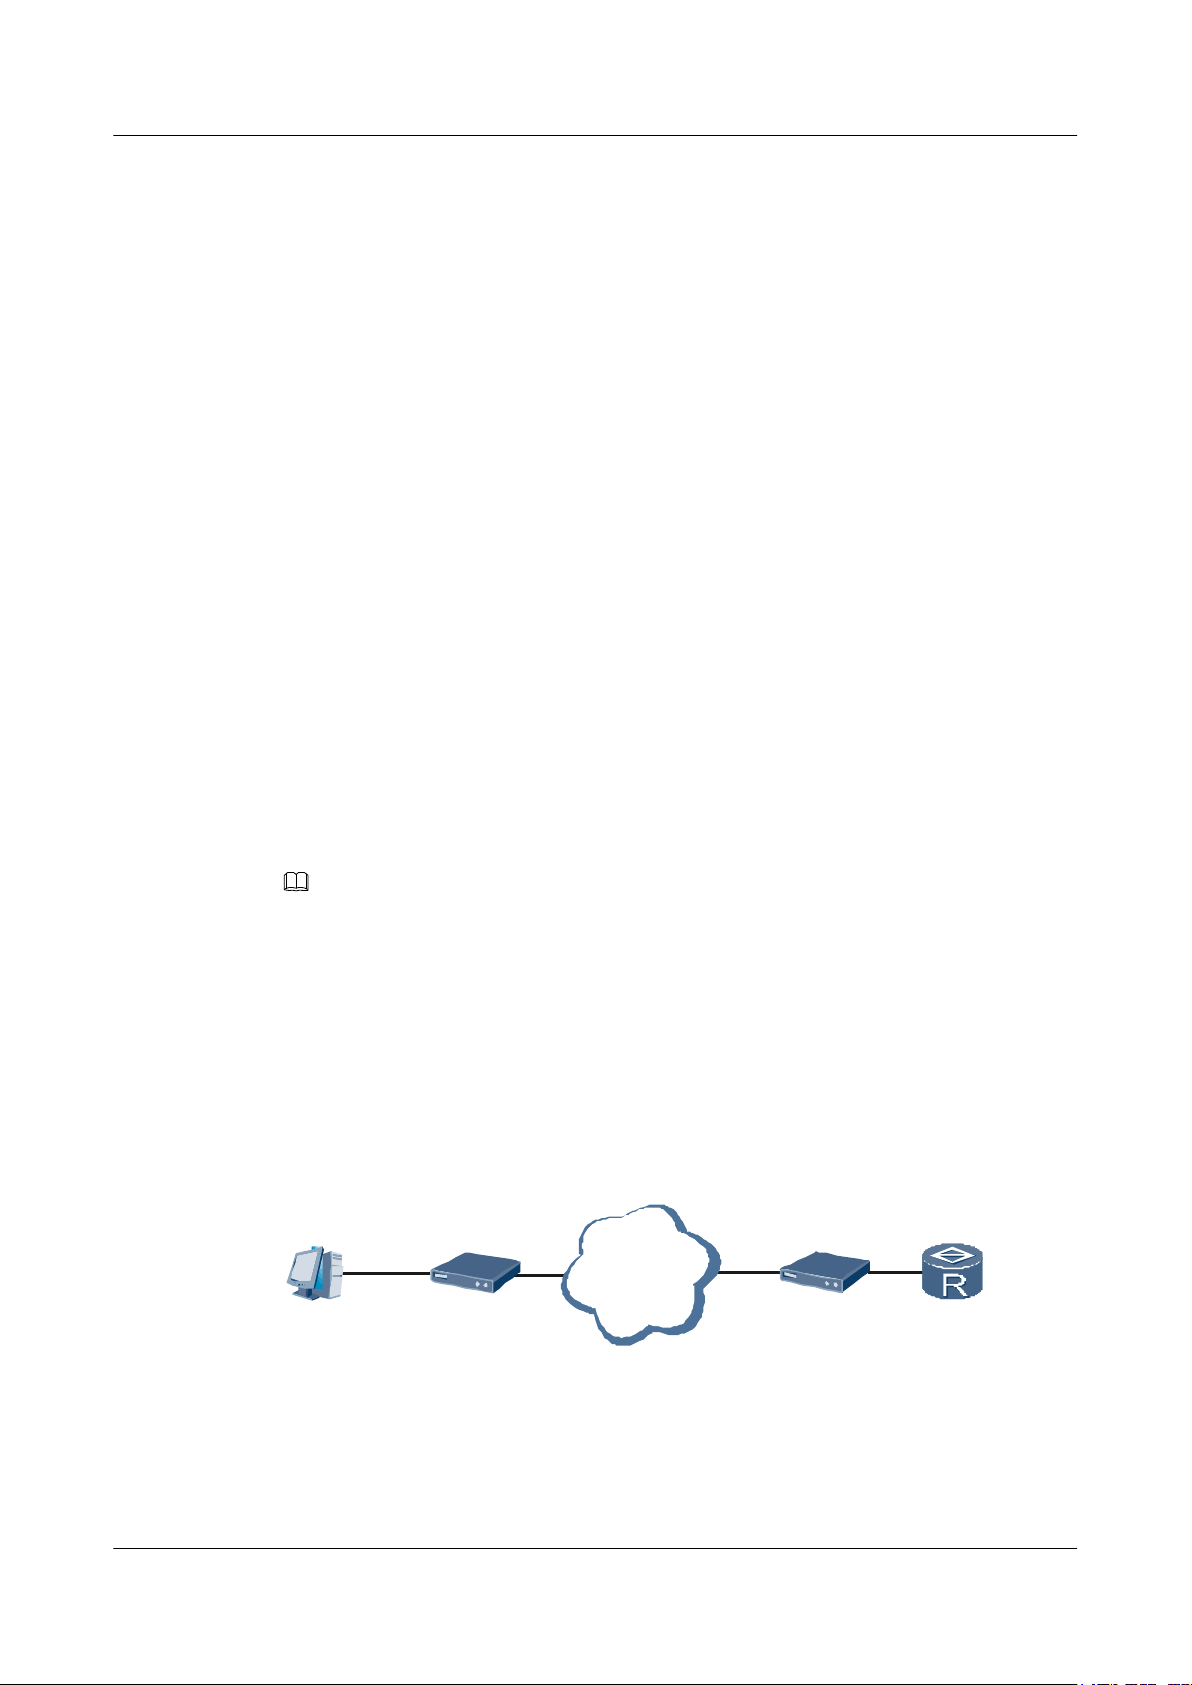
PSTN
PC RouterModem Modem
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
ll Active F Dft No 0
user1 Active F Dft No 0
----------------------------------------------------------------------------
Total 3,3 printed
5.3 Logging in to the Devices Through the AUX Port
When a user terminal and the router have no reachable route between each other, the user can
remotely configure and manage or locally maintain the router by logging in to the router through
an AUX port.
5.3.1 Establishing the Configuration Task
Before configuring user login through an AUX port, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This will help
you complete the configuration task quickly and accurately.
Applicable Environment
You can configure and maintain the router locally or remotely through an AUX port.
In local configuration of the router, the AUX login method is similar to the console login method.
The only difference between the two login methods lies in the default user priority: The default
user priority of the console user interface is 3, whereas that of the AUX user interface is 0.
Therefore, Logging in by using the console login method is recommended in the local
configuration. The following part mainly describes remote login of the router through an AUX
port.
NOTE
To manage and maintain the router through an AUX port, firstly modify the user priority of the AUX user
interface.
When there is no reachable route between a PC and the router, you can connect the serial port
of the PC to the AUX port of the router by using a modem. In this manner, you can use the PSTN
to configure and maintain the router remotely.
As shown in Figure 5-1, The COM interface of the PC is connected to the modem that is
connected to the PSTN. The AUX port of the router is connected to another modem that is
connected to the PSTN.
Figure 5-1 Networking diagram of remote login through an AUX port
Pre-configuration Tasks
Before configuring user login through an AUX port, complete the following tasks:
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
70
Page 86
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
l Connecting the PC to the router through modems
l Configuring the modem
l Installing a terminal emulator (such as HyperTerminal of Windows XP) in the PC
Data Preparation
To configure user login through an AUX port, you need the following data.
No. Data
1
2
l Transmission rate, flow control mode, parity, stop bit, data bit
l Number of lines displayed in a terminal screen, size of the history command buffer
l user priority
l modem attributes
l (Optional) Auto-run commands
l User authentication mode, user name, password
Telephone number of the modem at the remote router side.
5.3.2 Configuring AUX User Interface
To allow users to log in to the router through an AUX port, configure attributes of the AUX user
interface.
Context
Attributes of an AUX user interface have default values on the router, and generally need no
additional settings. To meet specific application requirements or ensure network security, you
can also set attributes of the AUX user interface, such as terminal attributes and user
authentication mode.
For detailed settings, see Configuring AUX User Interface.
5.3.3 Logging in to the routerThrough an AUX Port
You can establish a connection between a terminal and the router through an AUX port.
Procedure
Step 1 Start a terminal emulator (such as HyperTerminal of Windows XP) in the PC to establish a
connection with the router, as shown in Figure 5-2.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
71
Page 87
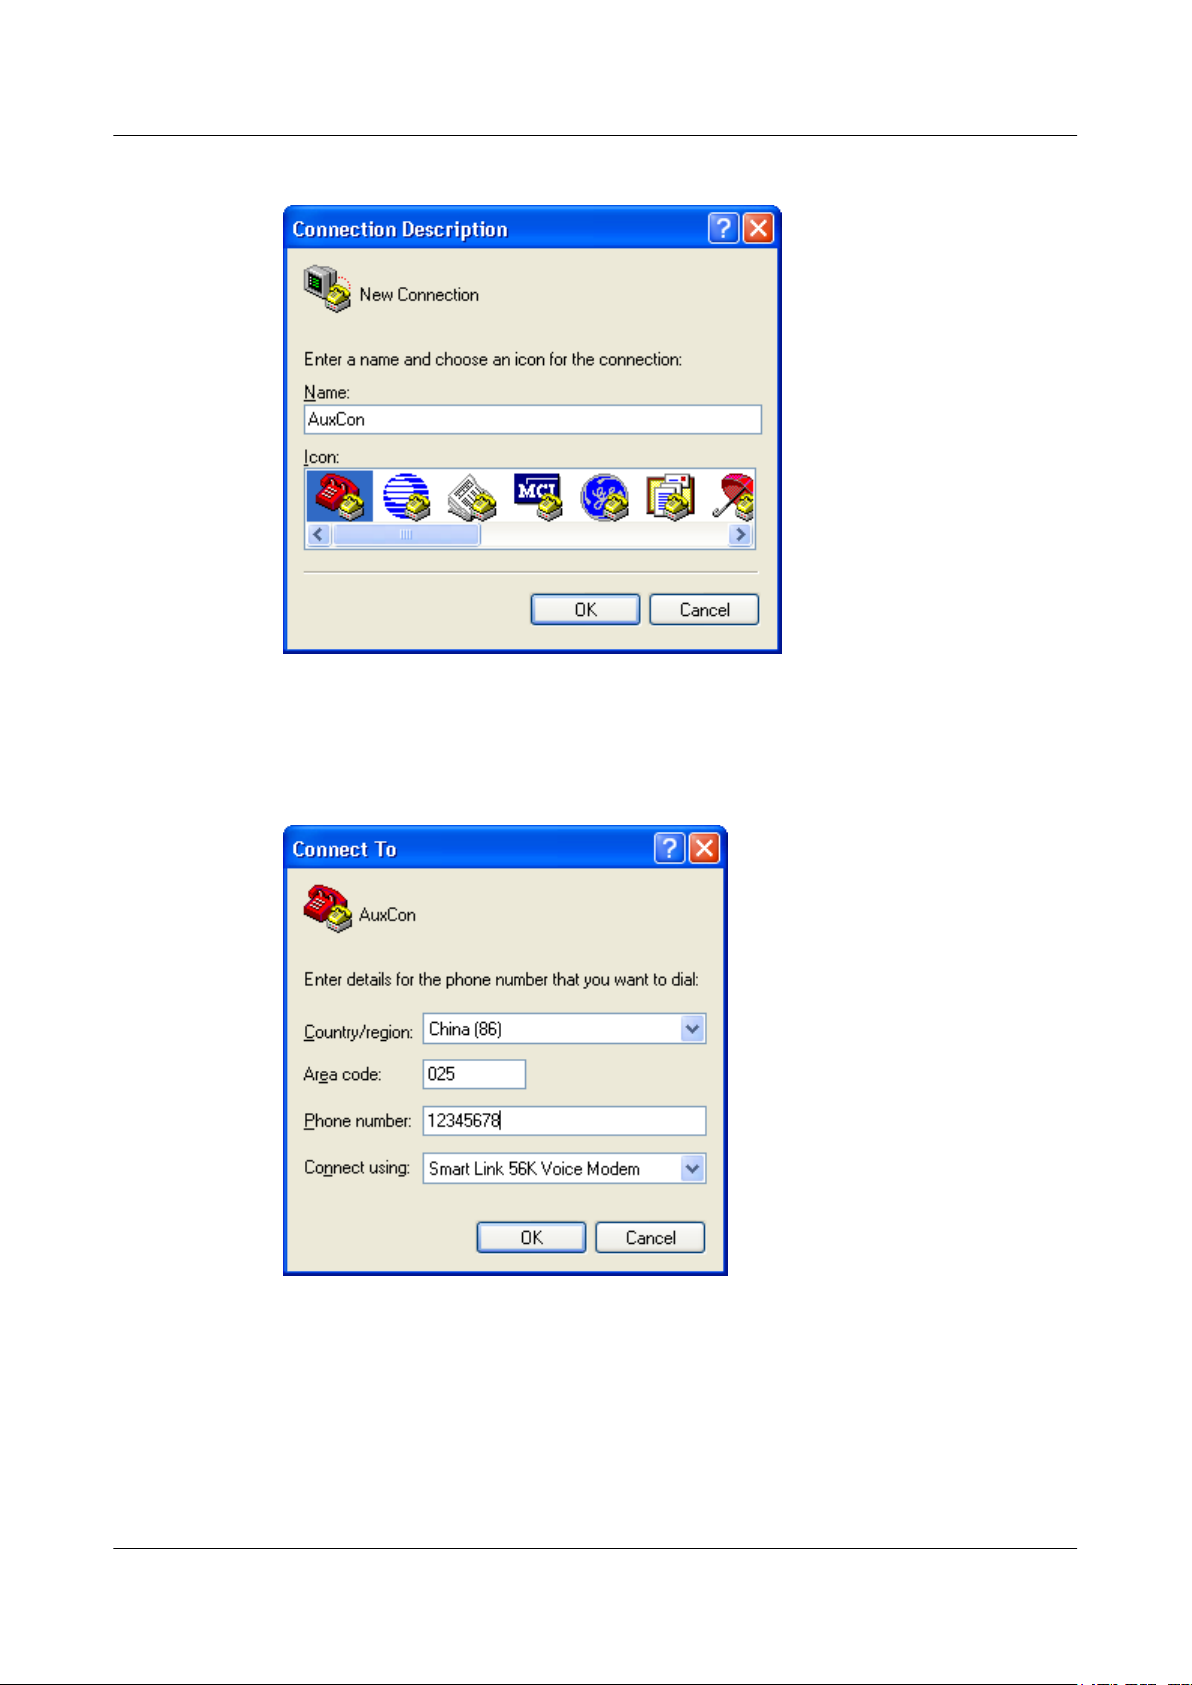
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
Figure 5-2 Connection creating
Step 2 Set dialing information, as shown in Figure 5-3.
Figure 5-3 Dialing information setting
Step 3 Establish a connection with the router, as shown in Figure 5-4.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
72
Page 88
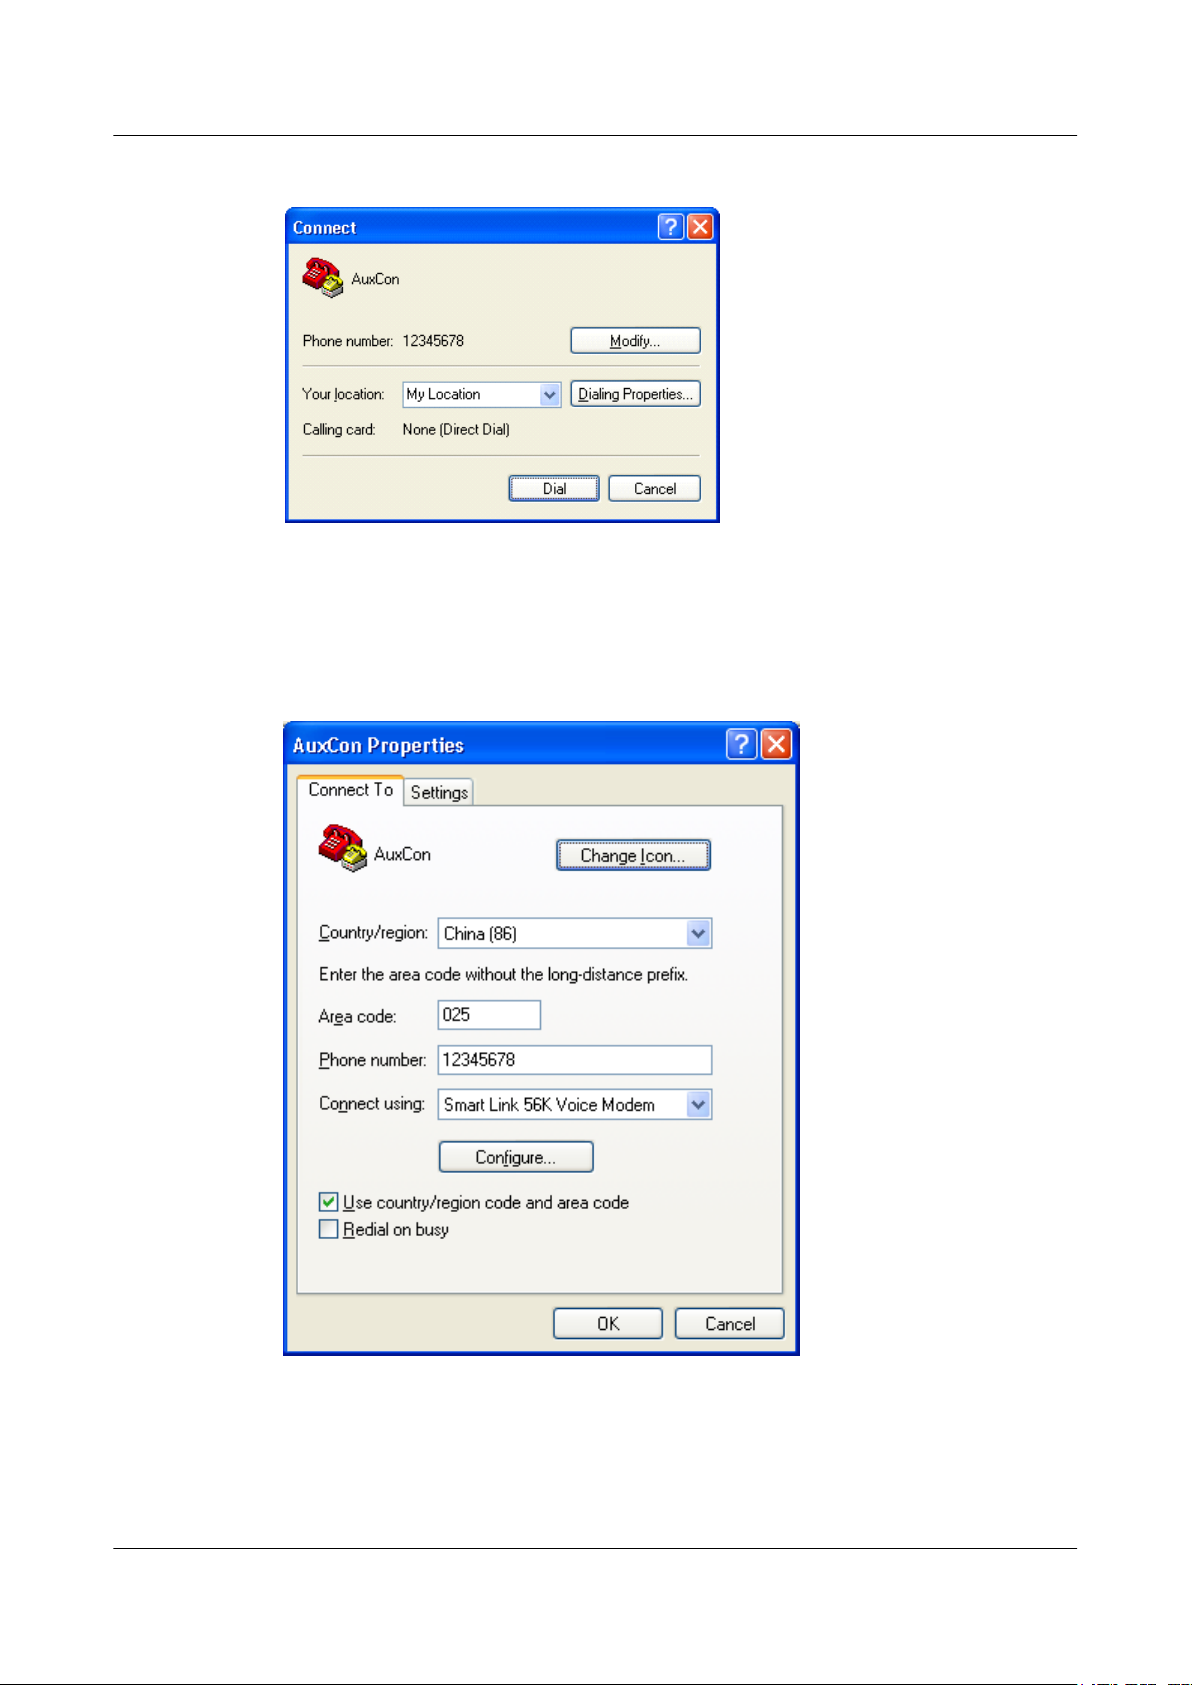
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
Figure 5-4 Remote connection with the router
If certain communication parameters need to be modified, press Modify in the Figure 5-4, as
shown in Figure 5-5, and then press Set, as shown in Figure 5-6.
Figure 5-5 Connection attribute modification
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
73
Page 89
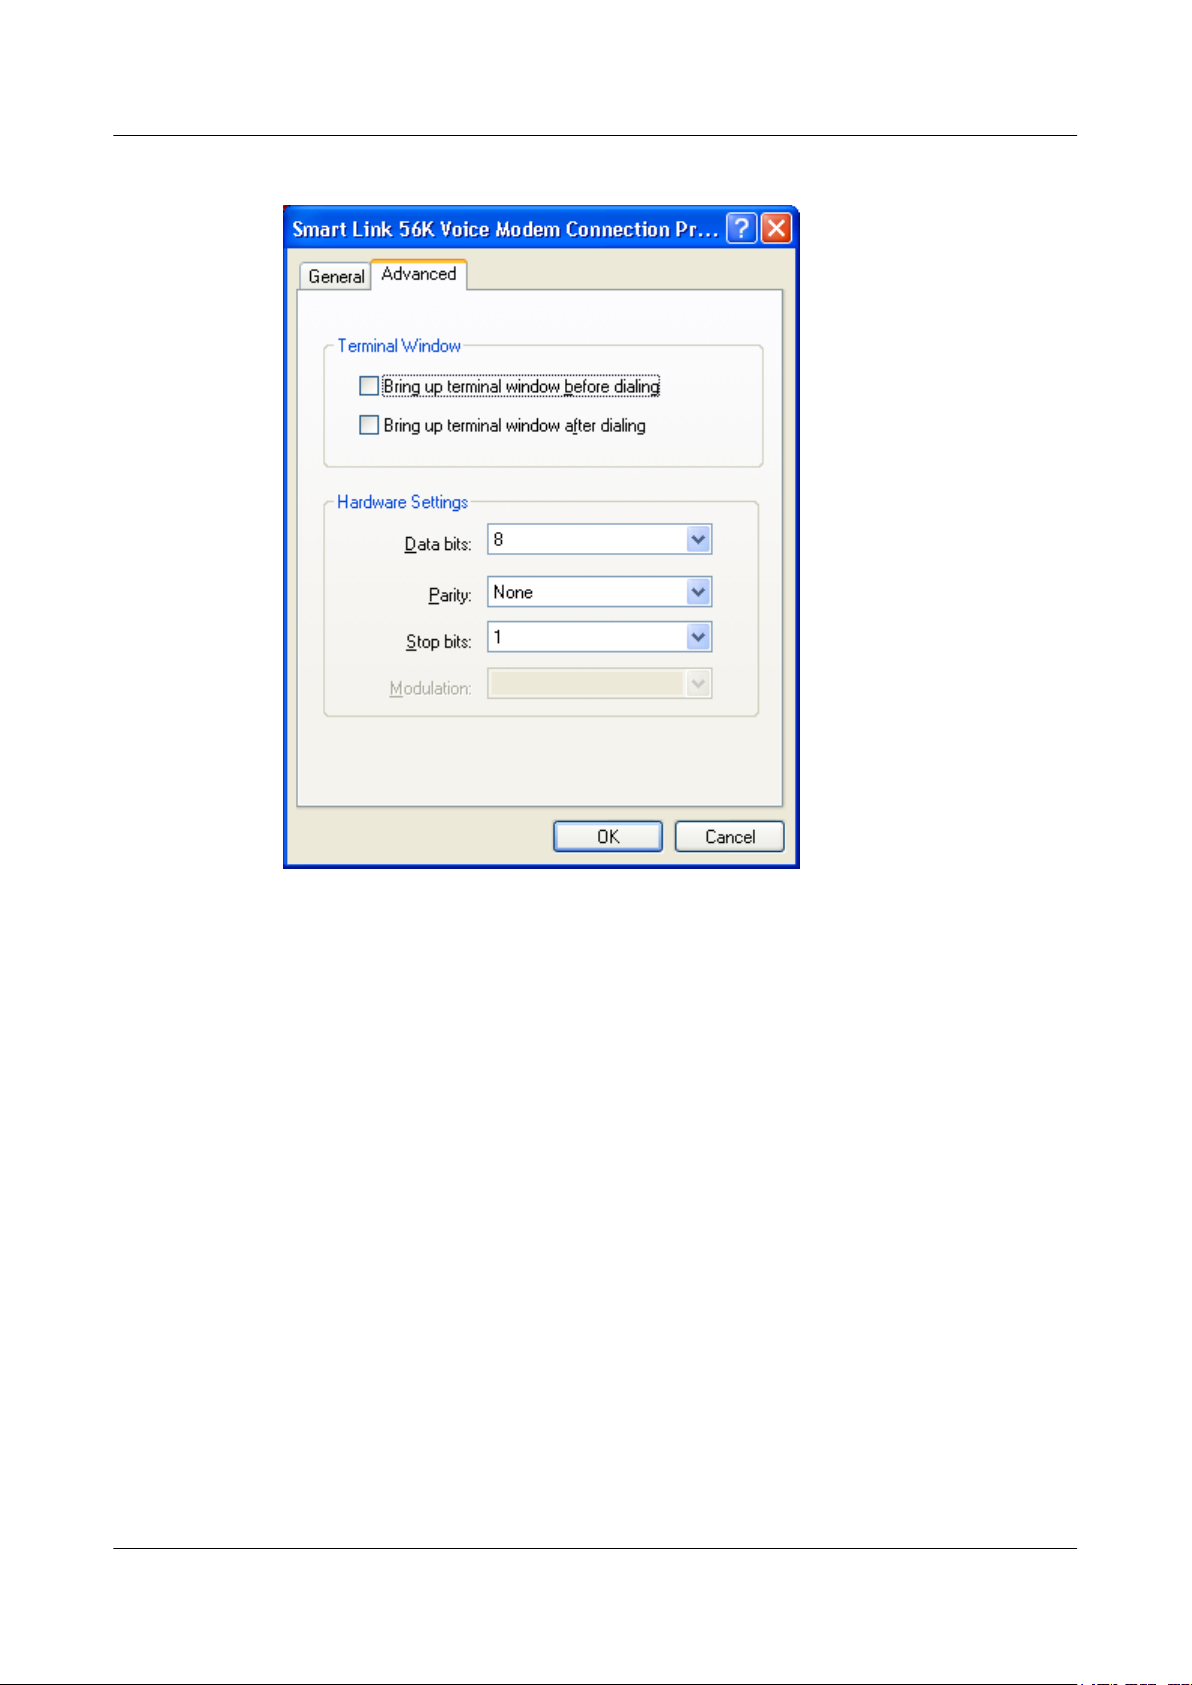
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
Figure 5-6 Communications parameters setting
Step 4 Press Dialing. If user authentication is needed, input the corresponding authentication
information, and wait till the command line prompt of the user view appears, such as
<HUAWEI>. This indicates that the user view is entered and relevant configurations can be
input.
----End
5.3.4 Checking the Configuration
After a user log in through an AUX port, the user can view information on the console user
interface, such as use information, physical attributes and configurations, local user list, and
online users.
Prerequisite
Configurations of user login through the AUX port are complete.
Procedure
l Run the display users [ all ] command to check usage information about the AUX user
interface.
l Run the display user-interface aux interface-number [ summary ] command to check
physical attributes and configurations of the user interface.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
74
Page 90
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
l Run the display local-user command to check the local user list.
l Run the display access-user command to check the local user list.
----End
Example
Run the display users command, and you can view information about the current user interface.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
33 AUX 0 00:00:44 pass no
Username : Unspecified
Run the display user-interface aux ui-number1 [ summary ] command, and you can view the
physical attributes and configurations of the user interface.
<HUAWEI> display user-interface aux 0
Idx Type Tx/Rx Modem Privi ActualPrivi Auth Int
33 AUX 0 9600 - 0 - N -
+ : Current UI is active.
F : Current UI is active and work in async mode.
Idx : Absolute index of UIs.
Type : Type and relative index of UIs.
Privi: The privilege of UIs.
ActualPrivi: The actual privilege of user-interface.
Auth : The authentication mode of UIs.
A: Authenticate use AAA.
N: Current UI need not authentication.
P: Authenticate use current UI's password.
Int : The physical location of UIs.
Run the display local-user command, and you can view the local user list.
<HUAWEI> display local-user
----------------------------------------------------------------------------
Username State Type CAR Access-limit Online
----------------------------------------------------------------------------
user123 Active All Dft No 0
ll Active F Dft No 0
user1 Active F Dft No 0
----------------------------------------------------------------------------
Total 3,3 printed
5.4 Logging in to the Devices by Using Telnet
If multiple routers need to be configured and managed, you do not need to connect the routers
and maintain them locally one by one. Instead, you can log in to the routers from a terminal by
using Telnet. This implements remote maintenance of the router and greatly facilitates device
management.
5.4.1 Establishing the Configuration Task
Before configuring user login by using Telnet, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This will help
you complete the configuration task quickly and accurately.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
75
Page 91
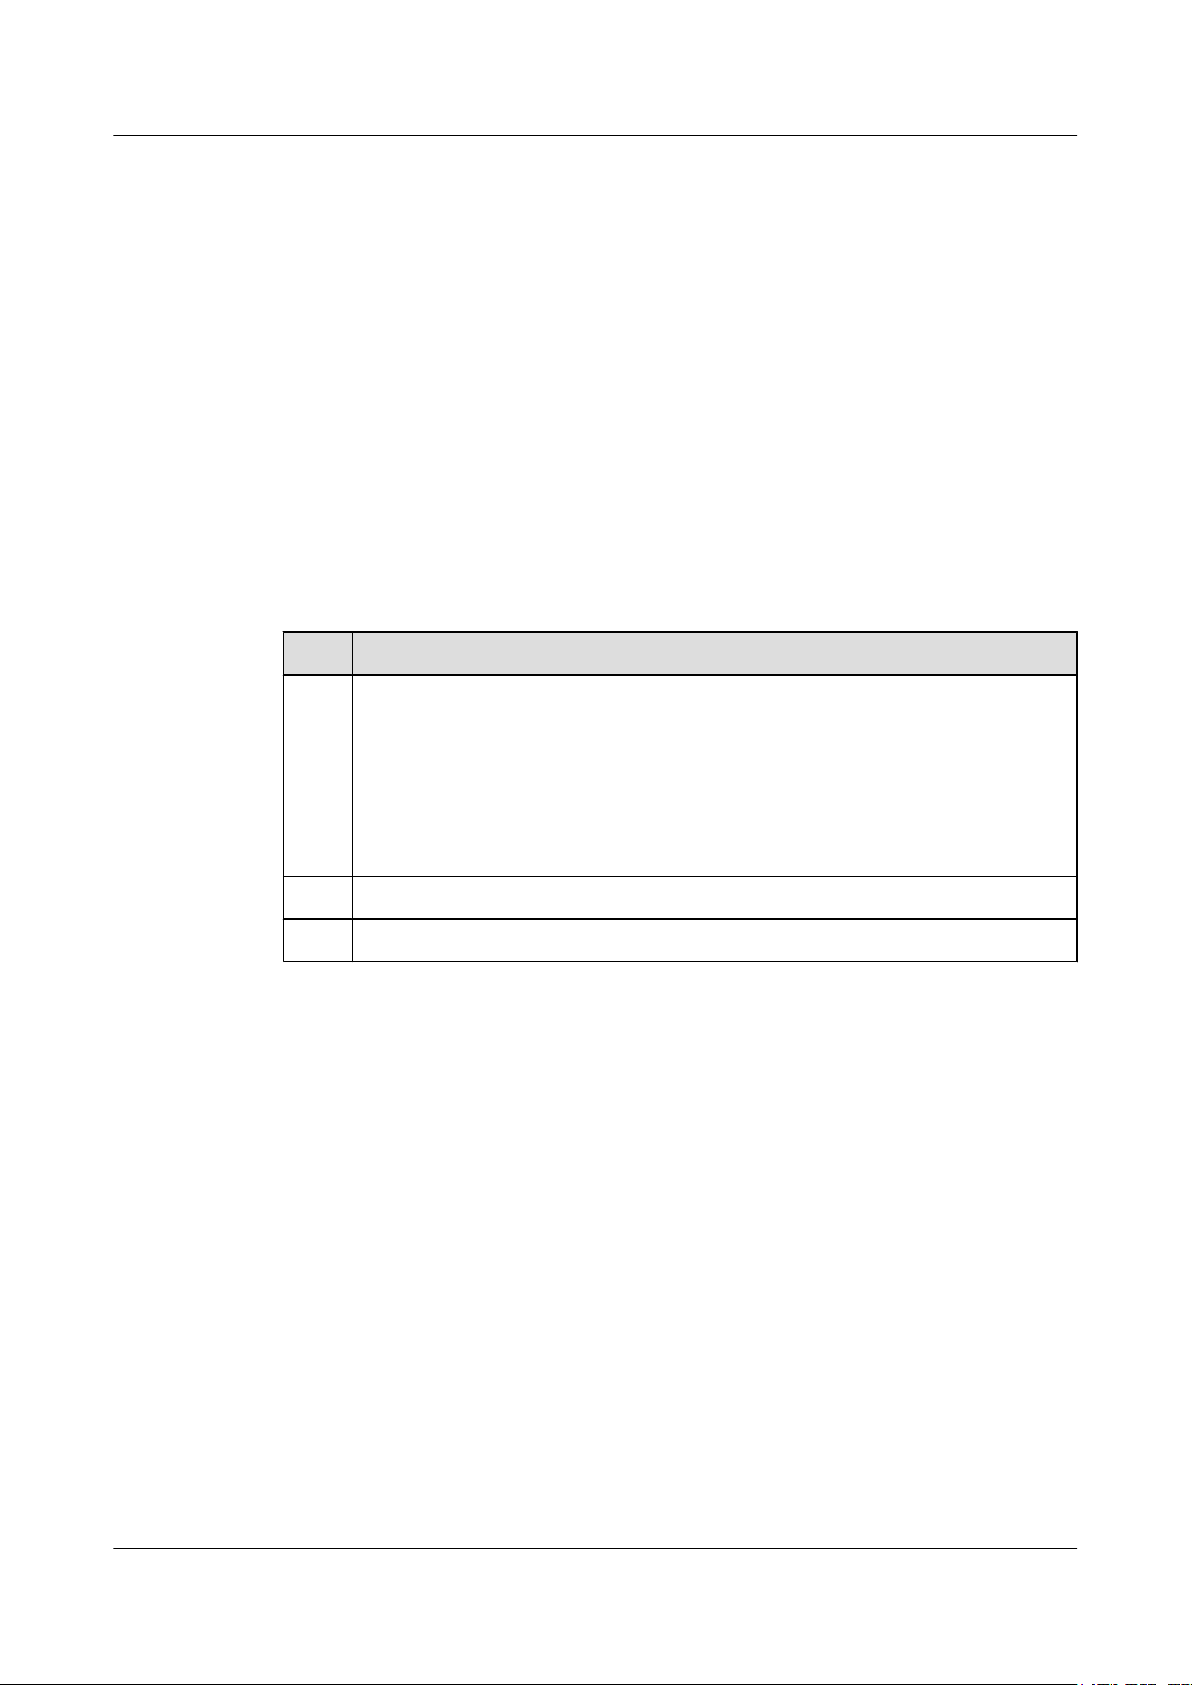
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
Applicable Environment
If you have known the IP address of the router to be accessed, you can log in to the router from
a terminal by using Telnet, and remotely maintain the device. This allows you to maintain
multiple routers on the same terminal, greatly facilitating device management.
Note that IP addresses of the routers need to be preset through console ports.
Pre-configuration Tasks
Before configuring user login in Telnet mode, complete the following tasks:
l Configuring reachable routes between the terminal and the device
Data Preparation
Before configuring user login in Telnet mode, you need the following data.
No. Data
1
2
3 IPv4/IPv6 address or host name of the router
l Maximum number of VTY user interfaces
l (Optional) ACL for limiting call-in and call-out in VTY user interfaces
l Connection timeout period of terminal users, number of lines displayed in a
terminal screen, size of the history command buffer
l User priority
l User authentication mode, user name, password
TCP port number for the remote router to provide Telnet services, VPN instance name
5.4.2 Configuring VTY User Interface
To log in to the router by using Telnet, configure attributes of the VTY user interface.
Context
By default, the user authentication mode in the VTY user interface is password. Therefore, before
a user logs in to the router by using Telnet, the user authentication mode in the VTY user interface
must be set. Otherwise, the user cannot log in to the router.
You can log in to the router through a console port to set the user authentication mode in the
VTY user interface.
Other attributes of the VTY user interface in the router, such as terminal attributes and user
priorities, can also be set as needed. These attributes, however, generally do not need to be set
because they have default values.
For detailed settings, see Configuring VTY User Interface.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
76
Page 92
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5.4.3 (Optional) Configuring Local Telnet Users
If the user authentication mode is AAA in the VTY user interface, the access type of local users
needs to be specified. Local users with the access type of Telnet are Telnet users.
Context
If the user authentication mode of the VTY user interface is non-authentication or password
authentication, the following configurations are not needed.
By default, a local user can apply for any access type. You can specify an access type to allow
only users configured with the specified access type to log in to the router.
Do as follows on the router that functions as a Telnet server:
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
aaa
The AAA view is displayed.
Step 3 Run:
local-user user-name password { simple | cipher } password
The local user name and password are set.
Step 4 Run:
local-user user-name service-type telnet
The access type of the local user is set to Telnet.
----End
5.4.4 Enabling the Telnet Service
Before a terminal establishes a Telnet connection with the router, enable the Telnet server
function on the router.
Context
By default, the function of the Telnet server is enabled.
Do as follows on the router that serves as an Telnet server.
Select and perform one of the following two steps for IPv4 or IPv6.
Procedure
l For the IPv4 network
1. Run:
system-view
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
77
Page 93
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
The system view is displayed.
2. Run:
telnet server enable
The Telnet service is enabled.
l For the IPv6 network
1. Run:
system-view
The system view is displayed.
2. Run:
telnet ipv6 server enable
The Telnet service is enabled.
NOTE
l If the undo telnet [ipv6] server enable command is run when a user logs in by using
Telnet, the command does not take effect.
l After the Telnet server function is disabled, you can log in to the device only using SSH
or an asynchronous serial port rather than using Telnet.
----End
5.4.5 (Optional) Configuring Listening Port Number for Telnet Server
A user can configure or change the listening port number of a Telnet server. Changing the
listening port number ensures network security, because only the user that knows the current
listening port number can log in to the router.
Context
By default, the listening port number of a Telnet server is 23. Users can directly log in to the
router using the default listening port number. Attackers may access the default listening port,
consuming bandwidth, deteriorating server performance, and causing authorized users unable
to access the server. After the listening port number of the Telnet server is changed, attackers
do not know the new listening port number. This effectively prevents attackers from accessing
the listening port.
Do as follows on the router that functions as a Telnet server:
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
telnet server port port-number
The listening port number of the Telnet server is set.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
78
Page 94
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
If a new listening port number is set, the Telnet server terminates all established Telnet
connections, and then uses the new port number to listen to new requests for Telnet connections.
----End
5.4.6 Logging in to the router by Using Telnet
After the router is configured, you can log in to the router from a terminal by using Telnet,
implementing remote maintenance of the router.
Context
If you need to log in to the router by using Telnet, you can use either windows command lines
or a third-party software in the terminal. In this part, the windows command line prompt is used.
Do as follows on the user terminal:
Procedure
Step 1 Use the windows command line.
Step 2 Run the telnet ip-address command to telnet the router.
1. Input the IP address of the Telnet server.
2. Press "Enter" to display the command line prompt of the system view, such as
<HUAWEI>. This indicates that you have accessed the Telnet server.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
79
Page 95
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
----End
5.4.7 Checking the Configuration
After users log in to the system by using Telnet, you can view the connection status of the current
user interface, connection status of each user interface, and status of all established TCP
connections.
Prerequisite
Configurations of logins by using Telnet are complete.
Procedure
l Run the display users [ all ] command to check information about logged-in users on user
interfaces.
l Run the display tcp status command to check TCP connections.
Example
l Run the display telnet server status command to check the configuration and status of the
Telnet server.
----End
Run the display users command to view information about the currently-used user interface.
<HUAWEI> display users
User-Intf Delay Type Network Address AuthenStatus AuthorcmdFlag
34 VTY 0 00:00:12 TEL 10.138.77.38 no
Username : Unspecified
+ 35 VTY 1 00:00:00 TEL 10.138.77.57 no
Username : Unspecified
Run the display tcp status command to view TCP connections. In the command output,
Established indicates that a TCP connection has been established.
<HUAWEI> display tcp status
TCPCB Tid/Soid Local Add:port Foreign Add:port VPNID
State
39952df8 36 /1509 0.0.0.0:0 0.0.0.0:0 0
Closed
32af9074 59 /1 0.0.0.0:21 0.0.0.0:0 14849
Listening
34042c80 73 /17 10.164.39.99:23 10.164.6.13:1147 0
Established
Run the display telnet server status command to view the configuration and status of the Telnet
server.
<HUAWEI> display telnet server status
Telnet IPV4 server :Enable
Telnet IPV6 server :Enable
Telnet server port :23
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
80
Page 96
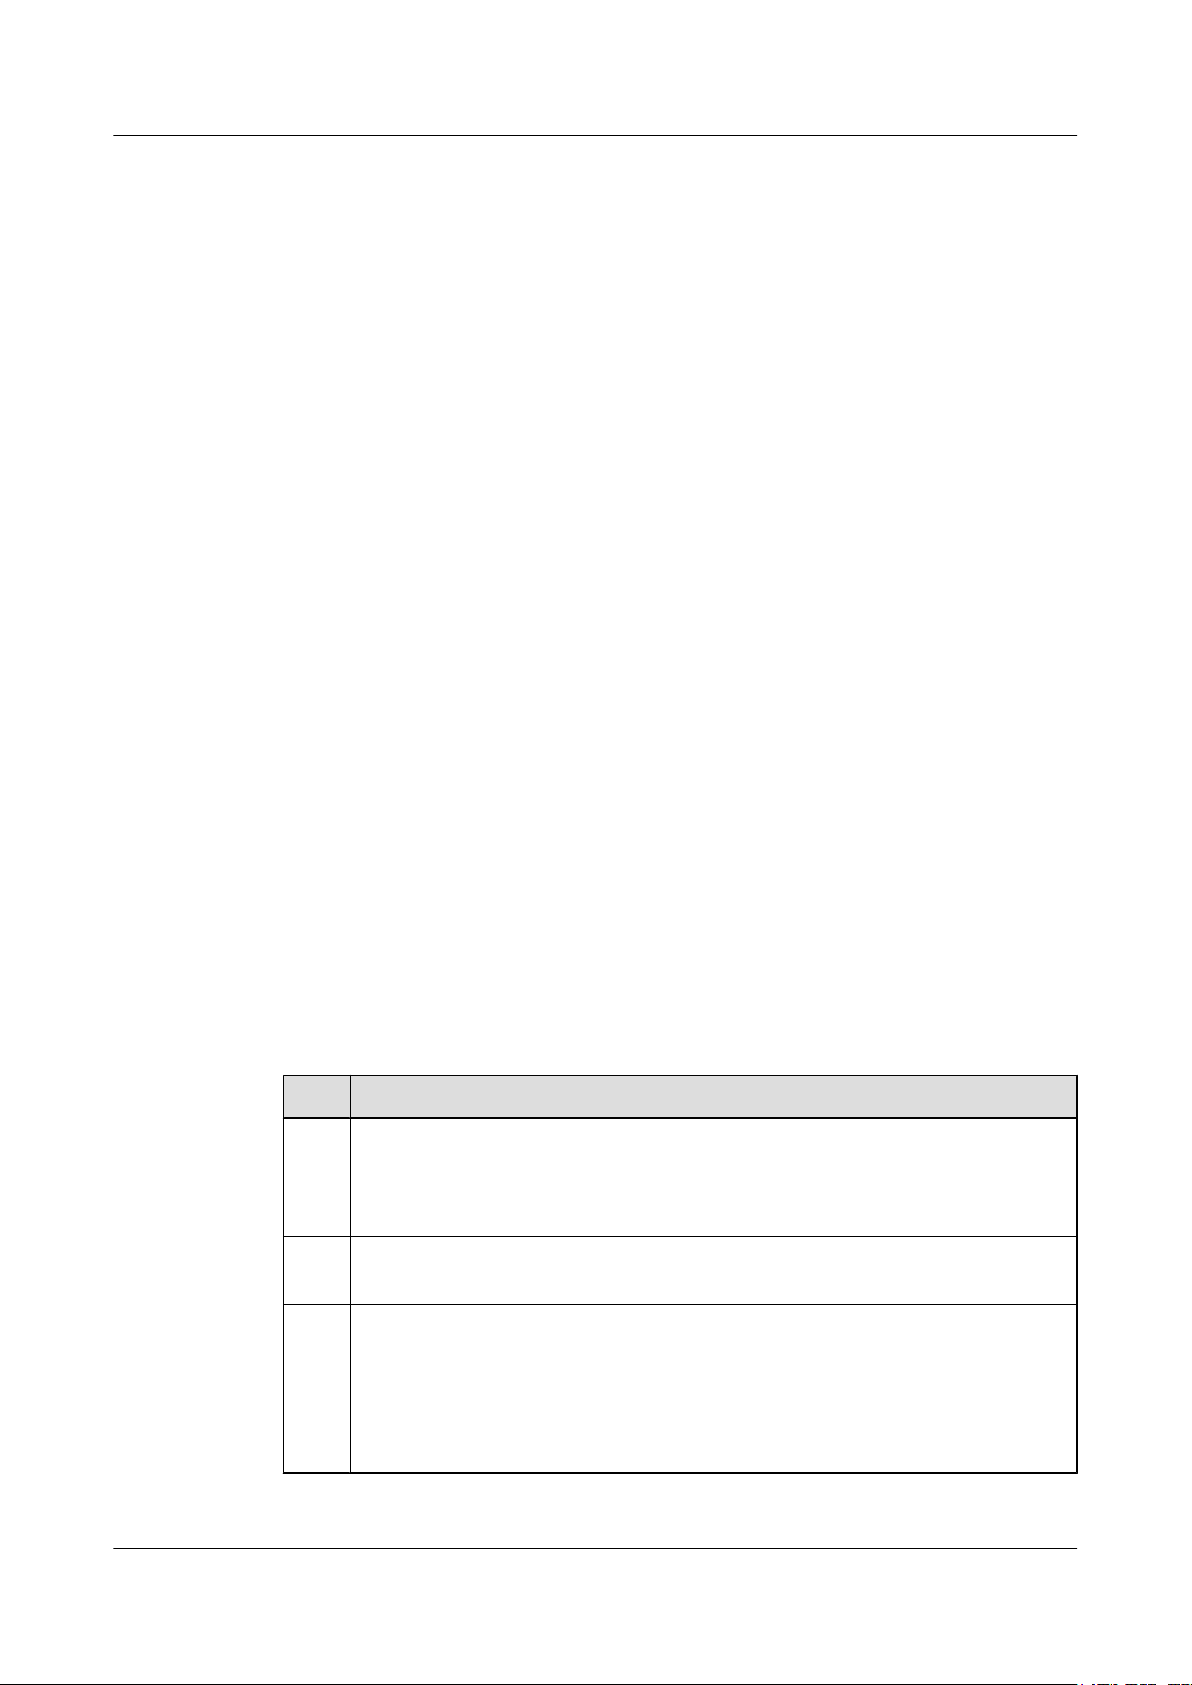
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5.5 Logging in to the Devices by Using STelnet
STelnet provides secured remote access over an insecure network. After the client/server
negotiation is complete and a secured connection is established, a user can log in to the router
in a similar way as Telnet.
5.5.1 Establishing the Configuration Task
Before configuring users to log in by using STelnet, familiarize yourself with the applicable
environment, complete the pre-configuration tasks, and obtain the required data. This will help
you complete the configuration task quickly and accurately.
Applicable Environment
Logins by using Telnet bring security risks because no secure authentication mechanism is
available and data is transmitted by using TCP in plain text mode. Unlike Telnet, SSH guarantees
secure data transmission on a conventional insecure network by authenticating the client and
encrypting data in both directions.
STelnet is a secure Telnet protocol. The SSH user can use the STelnet service in the same manner
as using the Telnet service.
Pre-configuration Tasks
Before configuring users to log in by using STelnet, complete the following task:
l Configuring reachable routes between the terminal and the device
Data Preparation
To configure users to log in by using STelnet, you need the following data:
No.
1 Maximum number of VTY user interfaces, (optional) ACL for limiting call-in and
2 User name, password, authentication mode, and service type of an SSH user and
3 (Optional) Name of an SSH server, number of the port monitored by the SSH server,
Data
call-out in VTY user interfaces, connection timeout period of terminal users, number
of rows displayed in a terminal screen, size of the history command buffer, user
authentication mode, user name, and password
remote public RSA key pair allocated to the SSH user
preferred encryption algorithm from the STelnet client to the SSH server, preferred
encrypted algorithm from the SSH server to the STelnet client, preferred HMAC
algorithm from the STelnet client to the SSH server, preferred HMAC algorithm from
the SSH server to the STelnet client, preferred algorithm of key exchange, name of
the outgoing interface, and source address
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
81
Page 97
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
5.5.2 Configuring VTY User Interface
To allow a user to log in to the router by using STelnet, configure attributes of the VTY user
interface.
Context
By default, the user authentication mode in the VTY user interface is password. Therefore, before
a user logs in to the router by using STelnet, the user authentication mode in the VTY user
interface must be set. Otherwise, the user cannot log in to the router.
You can log in to the router through a console port to set the user authentication mode in the
VTY user interface.
Other attributes of the VTY user interface in the router, such as terminal attributes and user
priorities, can also be set as needed. These attributes, however, generally do not need to be set
because they have default values.
For detailed settings, see Configuring VTY User Interface.
5.5.3 Configuring SSH for the VTY User Interface
To allow users to log in to the router by using STelnet, you need to configure VTY user interfaces
to support SSH.
Context
By default, user interfaces support Telnet. If no user interface is configured to support SSH,
users cannot log in to the router by using STelnet.
Do as follows on the router that serves as an SSH server:
Procedure
Step 1 Run:
system-view
The system view is displayed.
Step 2 Run:
user-interface [ vty ] first-ui-number [ last-ui-number ]
The VTY user interface is displayed.
Step 3 Run:
authentication-mode aaa
The AAA authentication mode is configured.
Step 4 Run:
protocol inbound ssh
The VTY user interface is configured to support SSH.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
82
Page 98
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
NOTE
If a VTY user interface is configured to support SSH, the VTY user interface must be configured with
AAA authentication. Otherwise, the protocol inbound ssh command cannot be configured.
----End
5.5.4 Configuring an SSH User and Specifying STelnet as One of Service Types
To allow a user to log in to the router by using STelnet, you must configure an SSH user,
configure the router to generate a local RSA key pair, configure a user authentication mode, and
specify a service type for the SSH user.
Context
l SSH users can be authenticated in four modes: RSA, password, password-RSA, and all.
Password authentication depends on Authentication, Authorization and Accounting
(AAA). Before a user logs in to the router in password or password-RSA authentication
mode, you must create a local user with the specified user name in the AAA view.
Procedure
Step 1 Run:
Step 2 Run:
l Configuring the router to generate a local RSA key pair is a key step for SSH login. If an
SSH user logs in to an SSH server in password authentication mode, configure the server
to generate a local RSA key pair. If an SSH user logs in to an SSH server in RSA
authentication mode, configure both the server and the client to generate local RSA key
pairs.
NOTE
Password-RSA authentication requires success of both password authentication and RSA authentication.
The all authentication mode requires success of either password authentication or RSA authentication.
Do as follows on the router that functions as an SSH server:
system-view
The system view is displayed.
ssh user user-name
1. Run:
aaa
The AAA view is displayed.
2. Run:
local-user user-name password { simple | cipher } password
Name and password of the local user are created.
Step 3 Run:
rsa local-key-pair create
A local RSA key pair is generated.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
83
Page 99
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
NOTE
l Before performing the other SSH configurations, you must configure the rsa local-key-pair create
command to generate a local key pair.
l After generating the local key pair,you can perform the display rsa local-key-pair public command
to view the public key in the local key pair.
Step 4 Run:
ssh user user-name authentication-type { password | rsa | password-rsa | all }
The authentication mode for SSH users is configured.
Perform the following as required:
l Authenticate the SSH user through the password.
– Run:
ssh user user-name authentication-type password
The password authentication is configured for the SSH user.
– Run:
ssh authentication-type default password
The default password authentication is configured for the SSH user.
For the local authentication or HWTACACS authentication, if the number of SSH users
is small, you can adopt the former command; if the number of SSH users is large, adopt
the later command to simplify the configuration.
l Authenticate the SSH user through RSA.
1. Run:
ssh user user-name authentication-type rsa
The RSA authentication is configured for the SSH user.
2. Run:
rsa peer-public-key key-name
The public key view is displayed.
3. Run:
public-key-code begin
The public key editing view is displayed.
4. Run:
hex-data
The public key is edited.
NOTE
l In the public key view, only hexadecimal strings complying with the public key format can be
typed in. Each string is randomly generated on an SSH client. For detailed operations, see manuals
for SSH client software.
l After the public key editing view is displayed, the RSA public key generated on the client can
be sent to the server. Copy the RSA public key to the router that serves as the SSH server.
5. Run:
public-key-code end
Quit the public key editing view.
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
84
Page 100
HUAWEI NetEngine80E/40E Router
Configuration Guide - Basic Configurations 5 Configuring User Login
l If the specified hex-data is invalid, the public key cannot be generated after the peer-
public-key end command is run.
l If the specified key-name is deleted in other views, the system prompts that the key does
not exist after the peer-public-key end command is run and the system view is
displayed.
6. Run:
peer-public-key end
Return to the system view from the public key view.
7. Run:
ssh user user-name assign rsa-key key-name
The public key is assigned to the SSH user.
Step 5 (Optional) Configuring the Basic Authentication Information for SSH Users
1. Run:
ssh server rekey-interval interval
The interval for updating the server key pair is configured.
By default, the interval for updating the key pair of the SSH server is 0 that indicates no
updating.
2. Run:
ssh server timeout seconds
The timeout period of the SSH authentication is set.
By default, the timeout period is 60 seconds.
3. Run:
ssh server authentication-retries times
The number of retry times of the SSH authentication is set.
By default, the retry times is 3.
Step 6 (Optional) Authorizing SSH Users Through the Command Line
SSH users can be authenticated in four modes: password, RSA, password-RSA, and all. In RSA
authentication mode, you can configure SSH users to be authorized based on command levels.
Run:
ssh user user-name authorization-cmd aaa
The command line authorization is configured for the specified SSH user.
After configuring the authorization through command lines for the SSH user to perform RSA
authentication, you have to configure the AAA authorization. Otherwise, the command line
authorization for the SSH user does not take effect.
Step 7 Run:
ssh user username service-type { stelnet | all }
The service type for the SSH user is configured.
By default, the service type of the SSH user is not configured.
----End
Issue 02 (2011-09-10) Huawei Proprietary and Confidential
Copyright © Huawei Technologies Co., Ltd.
85
 Loading...