

Page 1
1
0
Page 2
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
ii
Table of Contents
1. Introduction ............................................................................................................................................................. 1
2. Basic CLI Commands ........................................................................................................................................... 10
3. 802.1X Commands ............................................................................................................................................... 25
4. Access Control List (ACL) Commands ................................................................................................................. 38
5. Access Management Commands ........................................................................................................................ 66
6. ARP Spoofing Prevention Commands ................................................................................................................. 85
7. Asymmetric VLAN Commands ............................................................................................................................. 87
8. Authentication, Authorization, and Accounting (AAA) Commands ...................................................................... 88
9. Basic IPv4 Commands ....................................................................................................................................... 111
10. Basic IPv6 Commands ....................................................................................................................................... 118
11. BPDU Attack Protection Commands .................................................................................................................. 125
12. Cable Diagnostics Commands ........................................................................................................................... 129
13. Command Logging Commands ......................................................................................................................... 132
14. Debug Commands ............................................................................................................................................. 133
15. DHCP Auto-Configuration Commands ............................................................................................................... 146
16. DHCP Client Commands .................................................................................................................................... 148
17. DHCP Relay Commands .................................................................................................................................... 151
18. DHCP Snooping Commands ............................................................................................................................. 170
19. DHCPv6 Client Commands ................................................................................................................................ 188
20. DHCPv6 Guard Commands ............................................................................................................................... 190
21. DHCPv6 Relay Commands ................................................................................................................................ 194
22. Digital Diagnostics Monitoring (DDM) Commands ............................................................................................. 199
23. D-Link Discovery Protocol (DDP) Client Commands ......................................................................................... 208
24. Domain Name System (DNS) Commands ......................................................................................................... 211
25. DoS Prevention Commands ............................................................................................................................... 216
26. Dynamic ARP Inspection Commands ................................................................................................................ 220
27. Error Recovery Commands ................................................................................................................................ 233
28. Ethernet Ring Protection Switching (ERPS) Commands ................................................................................... 236
29. File System Commands ..................................................................................................................................... 249
30. Filter Database (FDB) Commands ..................................................................................................................... 255
31. GARP VLAN Registration Protocol (GVRP) Commands ................................................................................... 268
32. Gratuitous ARP Commands ............................................................................................................................... 276
33. IGMP Snooping Commands............................................................................................................................... 279
34. Interface Commands .......................................................................................................................................... 294
35. IP Source Guard Commands ............................................................................................................................. 307
36. IP Utility Commands ........................................................................................................................................... 313
37. IP-MAC-Port Binding (IMPB) Commands .......................................................................................................... 319
38. IPv6 Snooping Commands................................................................................................................................. 323
39. IPv6 Source Guard Commands ......................................................................................................................... 328
40. Japanese Web-based Access Control (JWAC) Commands .............................................................................. 334
41. Jumbo Frame Commands .................................................................................................................................. 345
Page 3
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
iii
42. Link Aggregation Control Protocol (LACP) Commands ..................................................................................... 346
43. Link Layer Discovery Protocol (LLDP) Commands ............................................................................................ 352
44. Loopback Detection (LBD) Commands .............................................................................................................. 379
45. MAC Authentication Commands ........................................................................................................................ 385
46. Mirror Commands ............................................................................................................................................... 389
47. MLD Snooping Commands ................................................................................................................................ 393
48. Multiple Spanning Tree Protocol (MSTP) Commands ....................................................................................... 408
49. Neighbor Discovery (ND) Inspection Commands .............................................................................................. 417
50. Network Access Authentication Commands ...................................................................................................... 421
51. Network Time Protocol (NTP) Commands ......................................................................................................... 434
52. Port Security Commands ................................................................................................................................... 448
53. Power over Ethernet (PoE) Commands ............................................................................................................. 454
54. Power Saving Commands .................................................................................................................................. 467
55. Protocol Independent Commands ...................................................................................................................... 473
56. Quality of Service (QoS) Commands ................................................................................................................. 479
57. Remote Network MONitoring (RMON) Commands ........................................................................................... 512
58. Router Advertisement (RA) Guard Commands ................................................................................................. 519
59. Safeguard Engine Commands ........................................................................................................................... 523
60. Secure Shell (SSH) Commands ......................................................................................................................... 530
61. Secure Sockets Layer (SSL) Commands .......................................................................................................... 537
62. sFlow Commands ............................................................................................................................................... 544
63. Simple Network Management Protocol (SNMP) Commands ............................................................................ 550
64. Single IP Management (SIM) Commands .......................................................................................................... 570
65. Spanning Tree Protocol (STP) Commands ........................................................................................................ 580
66. Stacking Commands .......................................................................................................................................... 592
67. Storm Control Commands .................................................................................................................................. 597
68. Surveillance VLAN Commands .......................................................................................................................... 602
69. Switch Port Commands ...................................................................................................................................... 608
70. System File Management Commands ............................................................................................................... 613
71. System Log Commands ..................................................................................................................................... 624
72. Time and SNTP Commands .............................................................................................................................. 632
73. Time Range Commands .................................................................................................................................... 638
74. Traffic Segmentation Commands ....................................................................................................................... 641
75. Virtual LAN (VLAN) Commands ......................................................................................................................... 643
76. Voice VLAN Commands ..................................................................................................................................... 656
77. Web Authentication Commands ......................................................................................................................... 663
Appendix A - System Log Entries ................................................................................................................................. 668
Appendix B - Trap Entries ............................................................................................................................................. 693
Appendix C - RADIUS Attributes Assignment ............................................................................................................... 703
Appendix D - IETF RADIUS Attributes Support ............................................................................................................ 706
Appendix E - ERPS Information .................................................................................................................................... 708
Page 4
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
1
1. Introduction
This manual’s command descriptions are based on the software release 1.30. The commands listed
here are the subset of commands that are supported by the DGS-1510 Series SmartPro Switch.
Audience
This CLI Reference Guide is intended for network administrators and other IT networking
professionals responsible for managing the switch by using the Command Line Interface (CLI). The
CLI is the primary management interface to the DGS-1510 Series SmartPro Switch, which will be
generally be referred to simply as “the Switch” within this manual. This manual is written in a way that
assumes that you already have the experience and knowledge of Ethernet and modern networking
principles for Local Area Networks.
Other Documentation
The documents below are a further source of information in regards to configuring and
troubleshooting the Switch. All the documents are available from the CD bundled with this switch, or
from the D-Link website. Other documents related to the Switch are:
DGS-1510 Series Gigabit Ethernet SmartPro Switch Hardware Installation Guide
DGS-1510 Series Gigabit Ethernet SmartPro Switch Web UI Reference Guide
Conventions
Convention
Description
Boldface Font
Commands, command options and keywords are printed in
boldface. Keywords, in the command line, are to be entered exactly
as they are displayed.
UPPERCASE ITALICS Font
Parameters or values that must be specified are printed in
UPPERCASE ITALICS. Parameters in the command line are to be
replaced with the actual values that are desired to be used with the
command.
Square Brackets [ ]
Square brackets enclose an optional value or set of optional
arguments.
Braces { }
Braces enclose alternative keywords separated by vertical bars.
Generally, one of the keywords in the separated list can be chosen.
Vertical Bar |
Optional values or arguments are enclosed in square brackets and
separated by vertical bars. Generally, one or more of the vales or
arguments in the separated list can be chosen.
Blue Courier Font
This convention is used to represent an example of a screen
console display including example entries of CLI command input
with the corresponding output. All examples used in this manual are
based on the DGS-1510-28P switch.
Notes, Notices, and Cautions
Below are examples of the three types of indicators used in this manual. When administering your
switch using the information in this document, you should pay special attention to these indicators.
Each example below provides an explanatory remark regarding each type of indicator.
Page 5
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
2
NOTE: A note indicates important information that helps you make better use of your
device.
NOTICE: A notice indicates either potential damage to hardware or loss of data and tells
you how to avoid the problem.
CAUTION: A caution indicates a potential for property damage, personal injury, or death.
Command Descriptions
The information pertaining to each command in this reference guide is presented using a number of
template fields. The fields are:
Description - This is a short and concise statement describing the commands functionality.
Syntax - The precise form to use when entering and issuing the command.
Parameters - A table where each row describes the optional or required parameters, and
their use, that can be issued with the command.
Default - If the command sets a configuration value or administrative state of the Switch then
any default settings (i.e. without issuing the command) of the configuration is shown here.
Command Mode - The mode in which the command can be issued. These modes are
described in the section titled “Command Modes” below.
Command Default Level – The user privilege level in which the command can be issued.
Usage Guideline - If necessary, a detailed description of the command and its various
utilization scenarios is given here.
Example(s) - Each command is accompanied by a practical example of the command being
issued in a suitable scenario.
Command Modes
There are several command modes available in the command-line interface (CLI). The set of
commands available to the user depends on both the mode the user is currently in and their privilege
level. For each case, the user can see all the commands that are available in a particular command
mode by entering a question mark (?) at the system prompt.
The command-line interface has three pre-defined privilege levels:
Basic User - Privilege Level 1. This user account level has the lowest priority of the user
accounts. The purpose of this type of user account level is for basic system checking.
Operator - Privilege Level 12. This user account level is used to grant system configuration
rights for users who need to change or monitor system configuration, except for security
related information such as user accounts and SNMP account settings, etc.
Administrator - Privilege Level 15. This administrator user account level can monitor all
system information and change any of the system configuration settings expressed in this
configuration guide.
The command-line interface has a number of command modes. There are three basic command
modes:
User EXEC Mode
Privileged EXEC Mode
Global Configuration Mode
Page 6
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
3
All other sub-configuration modes can be accessed via the Global Configuration Mode.
When a user logs in to the Switch, the privilege level of the user determines the command mode the
user will enter after initially logging in. The user will either log into User EXEC Mode or the Privileged
EXEC Mode.
Users with a basic user level will log into the Switch in the User EXEC Mode.
Users with operator or administrator level accounts will log into the Switch in the Privileged
EXEC Mode.
Therefore, the User EXEC Mode can operate at a basic user level and the Privileged EXEC Mode can
operate at the operator, or administrator levels. The user can only enter the Global Configuration
Mode from the Privileged EXEC Mode. The Global Configuration Mode can be accessed by users
who have operator or administrator level user accounts.
As for sub-configuration modes, a subset of those can only be accessed by users who have the
highest secure administrator level privileges.
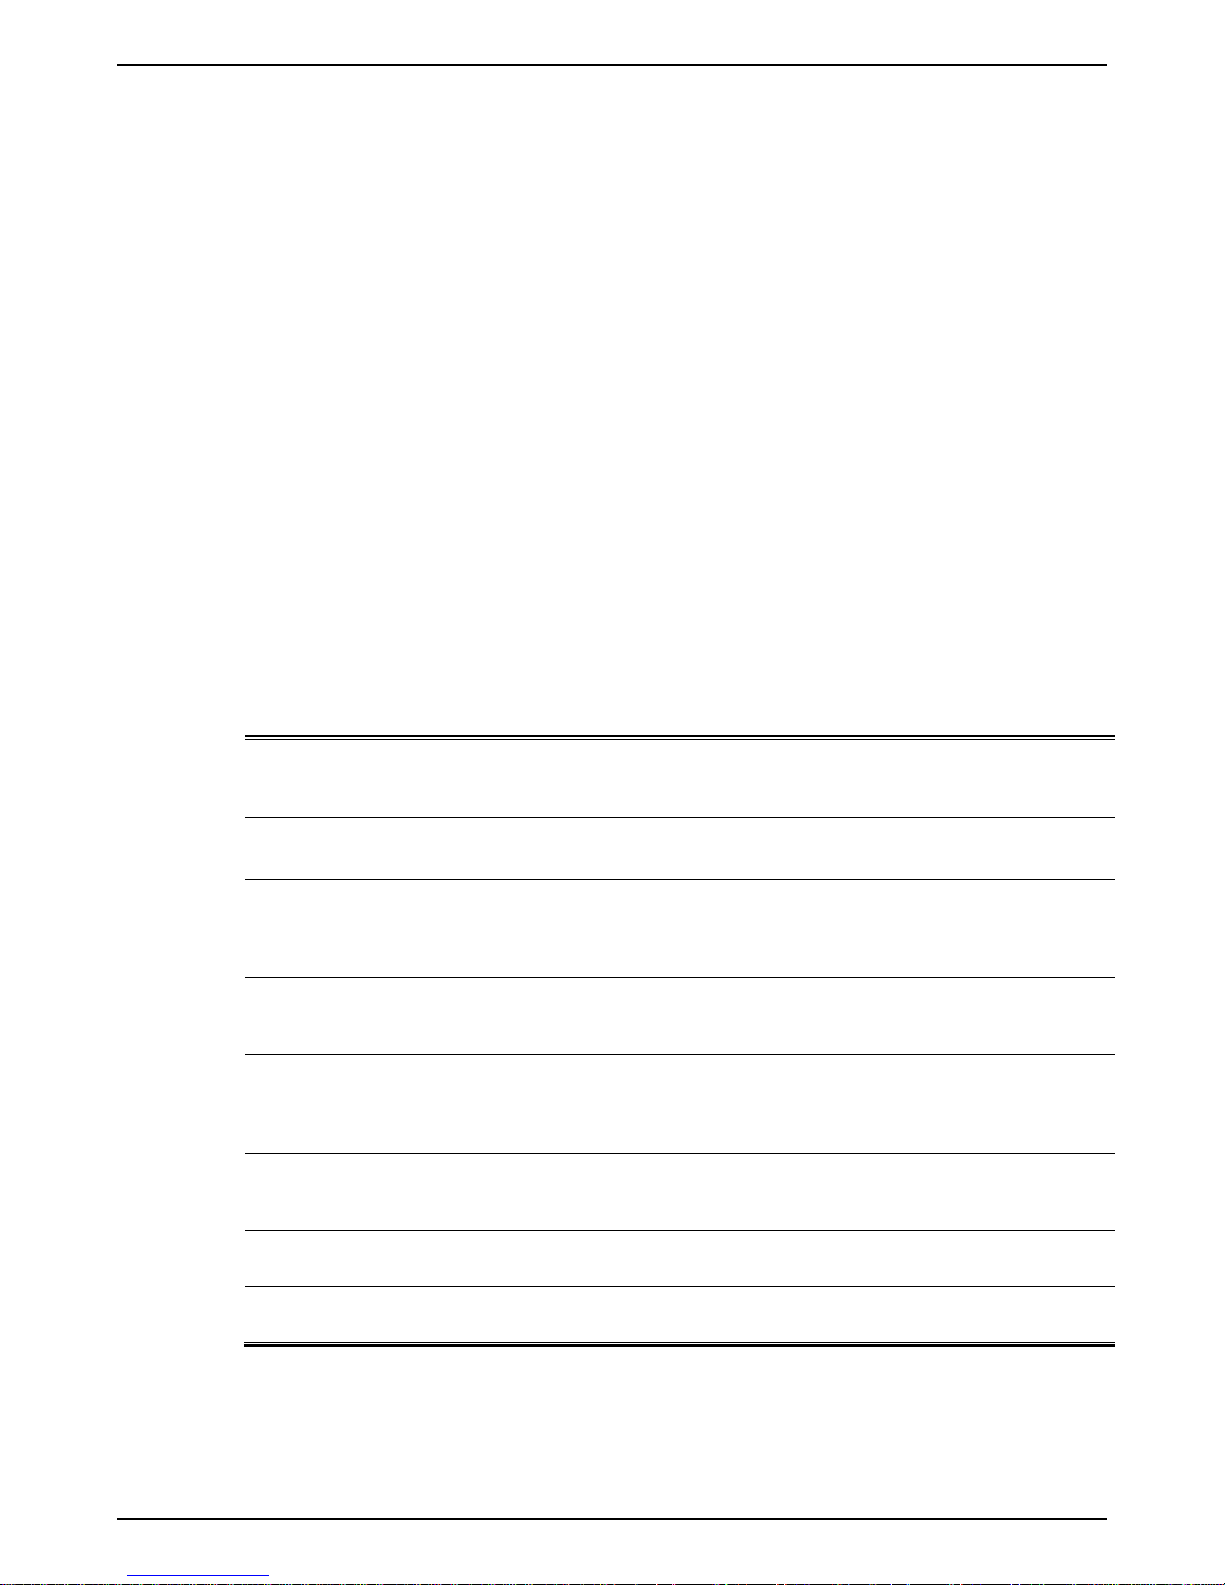
The following table briefly lists the available command modes. Only the basic command modes and
some of the sub-configuration modes are enumerated. The basic command modes and basic subconfiguration modes are further described in the following chapters. Descriptions for the rest of the
sub-configuration modes are not provided in this section. For more information on the additional subconfiguration modes, the user should refer to the chapters relating to these functions.
The available command modes and privilege levels are described below:
Command Mode /
Privilege Level
Purpose
User EXEC Mode /
Basic User level
This level has the lowest priority of the user accounts. It is provided
only to check basic system settings.
Privileged EXEC Mode /
Operator level
For changing both local and global terminal settings, monitoring, and
performing certain system administration tasks. The system
administration tasks that can be performed at this level except for any
security related information.
Privileged EXEC Mode /
Administrator level
This level is identical to privileged EXEC mode at the operator level,
except that a user at the administrator level can monitor and clear
security related settings.
Global Configuration Mode /
Operator level
For applying global settings, except for security related settings, on
the entire switch. In addition to applying global settings on the entire
switch, the user can access other sub-configuration modes from
global configuration mode.
Global Configuration Mode /
Administrator level
For applying global settings on the entire switch. In addition to
applying global settings on the entire switch, the user can access
other sub-configuration modes from global configuration mode.
Interface Configuration Mode
/ Administrator level
For applying interface related settings.
VLAN Interface Configuration
Mode
For applying VLAN interface related settings.
User EXEC Mode at Basic User Level
This command mode is mainly designed for checking basic system settings. This command mode can
be entered by logging in as a basic user.
Privileged EXEC Mode at Operator Level
Page 7
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
4
Users logged into the Switch in privileged EXEC mode at this level can change both local and global
terminal settings, monitor, and perform system administration tasks (except for security related
information). The method to enter privileged EXEC mode at operator level is to login to the Switch
with a user account that has a privilege level of 12.
Privileged EXEC Mode at Administrator Level
This command mode has a privilege level of 15. Users logged in with this command mode can
monitor all system information and change any system configuration settings mentioned in this
Configuration Guide. The method to enter privileged EXEC mode at administrator level is to login to
the Switch with a user account that has a privilege level of 15.
Global Configuration Mode
The primary purpose of the global configuration mode is to apply global settings on the entire switch.
Global configuration mode can be accessed at operator or administrator level user accounts. However,
security related settings are not accessible at operator user account. In addition to applying global
settings on the entire switch, the user can also access other sub-configuration modes. In order to
access the global configuration mode, the user must be logged in with the corresponding account
level and use the configure terminal command in the privileged EXEC mode.
In the following example, the user is logged in as an Administrator in the Privileged EXEC Mode and
uses the configure terminal command to access the Global Configuration Mode:
Switch# configure terminal
Switch(config)#
The exit command is used to exit the global configuration mode and return to the privileged EXEC
mode.
Switch(config)# exit
Switch#
The procedures to enter the different sub-configuration modes can be found in the related chapters in
this Configuration Guide. The command modes are used to configure the individual functions.
Interface Configuration Mode
Interface configuration mode is used to configure the parameters for an interface or a range of
interfaces. An interface can be a physical port, VLAN, or other virtual interface. Thus, interface
configuration mode is distinguished further according to the type of interface. The command prompt
for each type of interface is slightly different.
VLAN Interface Configuration Mode
VLAN interface configuration mode is one of the available interface modes and is used to configure
the parameters of a VLAN interface.
To access VLAN interface configuration mode, use the following command in global configuration
mode:
Switch(config)# interface vlan 1
Switch(config-if)#
Creating a User Account
You can create different user account for various levels. This section will assist a user with creating a
user account by means of the Command Line Interface.
NOTE: By default, one user account is already configured on the Switch. Both the
username and password for this account is admin, and the privilege level is 15.
Page 8

DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
5
Observe the following example.
Switch>enable
Switch#configure terminal
Switch(config)#username user1 password pass1234
Switch(config)#username user1 privilege 15
Switch(config)#line console
Switch(config-line)#login local
Switch(config-line)#
In the above example we had to navigate and access the username command.
Starting in the User EXEC Mode we enter the command enable to access the Privileged
EXEC Mode.
After accessing the Privileged EXEC Mode, we entered the command configure terminal to
access the Global Configuration Mode. The username command can be used in the Global
Configuration Mode.
The command username user1 password pass1234 creates a user account with the
username of user1 and a password of pass1234.
The command username user1 privilege 15 assigns a privilege level value of 15 to the user
account admin.
The command line console allows us to access the console interface’s Line Configuration
Mode.
The command login local tell the Switch that users need to enter locally configured login
credentials to access the console interface.
Save the running configuration to the start-up configuration. This means to save the changes made so
that when the Switch is rebooted, the configuration will not be lost. The following example shows how
to save the running configuration to the start-up configuration.
Switch#copy running-config startup-config
Destination filename startup-config? [y/n]: y
Saving all configurations to NV-RAM.......... Done.
Switch#
After the Switch was rebooted, or when the users logs out and back in, the newly created username
and password must be entered to access the CLI interface again, as seen below.
DGS-1510-28XMP Gigabit Ethernet SmartPro Switch
Command Line Interface
Firmware: Build 1.30.003
Copyright(C) 2015 D-Link Corporation. All rights reserved.
User Access Verification
Username:user1
Password:********
Switch#
Page 9

DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
6
Interface Notation
When configuration the physical ports available on this switch, a specific interface notation is used.
The following will explain the layout, terminology and use of this notation.
In the following example, we will enter the Global Configuration Mode and then enter the Interface
Configuration Mode, using the notation 1/0/1. After entering the Interface Configuration Mode for port
1, we will change the speed to 1 Gbps, using the speed 1000 command.
Switch# configure terminal
Switch(config)# interface Ethernet 1/0/1
Switch(config-if)# speed 1000
Switch(config-if)#
In the above example the notation 1/0/1 was used. The terminology for each parameter is as follows:
Interface Unit’s ID / Open Slot’s ID / Port’s ID
The Interface Unit’s ID is the ID of the stacking unit without the physical stack. If stacking is disabled
or this unit is a stand-alone unit, then this parameter is irrelevant. The Open Slot’s ID is the ID of the
module plugged into the open module slot of the Switch. The DGS-1510 Series does not support any
open modules slots, thus this parameters will always by zero for this switch series. Lastly, the Port’s
ID is the physical port number of the port being configured.
In summary the above example will configure the stacked switch with the ID of 1, with the open slot ID
of 0, and the physical port number 1.
Error Messages
When the users issue a command that the Switch does not recognize, error messages will be
generated to assist users with basic information about the mistake that was made. A list of possible
error messages are found in the table below.
Error Message
Meaning
Ambiguous command
Not enough keywords were entered for the Switch to recognize the
command.
Incomplete command
The command was not entered with all the required keyword.
Invalid input detected at
^marker
The command was entered incorrectly.
The following example shows how an ambiguous command error message is generated.
Switch# show v
Ambiguous command
Switch#
The following example shows how an incomplete command error message is generated.
Switch# show
Incomplete command
Switch#
The following example shows how an invalid input error message is generated.
Page 10
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
7
Switch# show verb
^
Invalid input detected at ^marker
Switch#
Editing Features
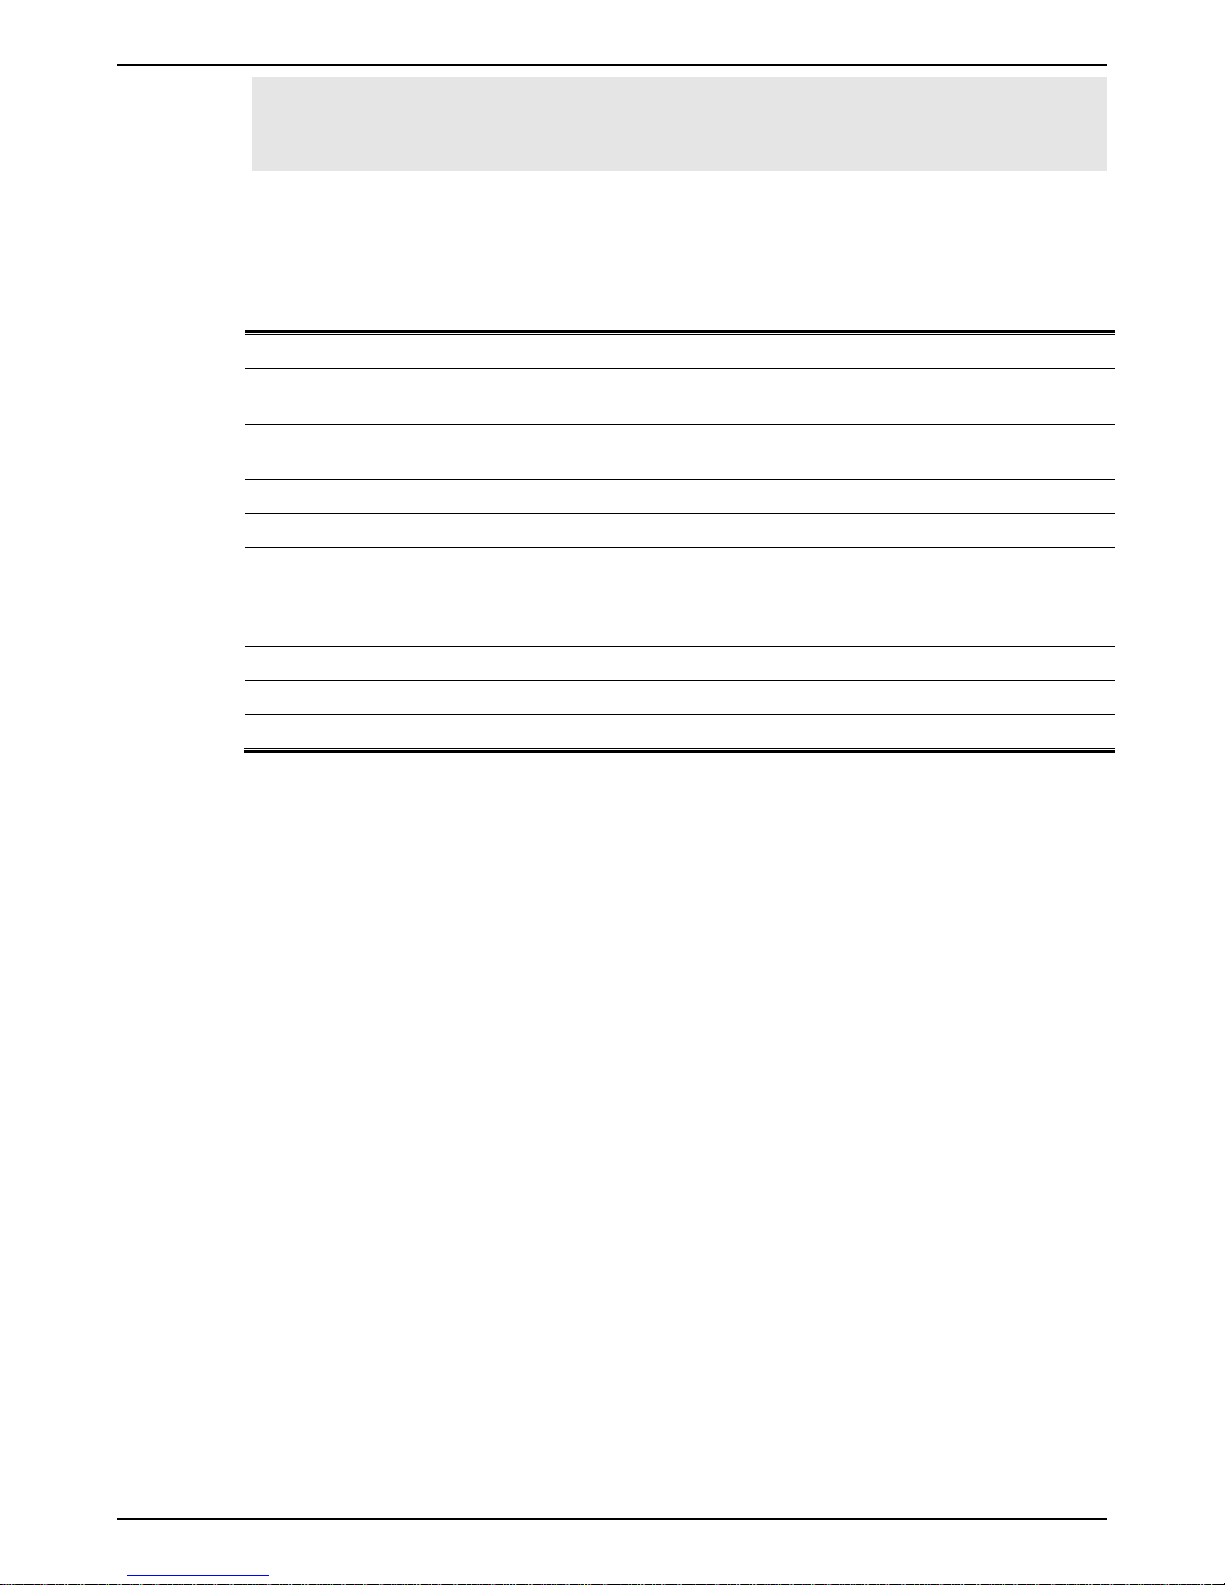
The command line interface of this switch supports to following keyboard keystroke editing features.
Keystroke
Description
Delete
Deletes the character under the cursor and shifts the remainder of
the line to the left.
Backspace
Deletes the character to the left of the cursor and shifts the
remainder of the line to the left.
Left Arrow
Moves the cursor to the left.
Right Arrow
Moves the cursor to the right.
CTRL+R
Toggles the insert text function on and off. When on, text can be
inserted in the line and the remainder of the text will be shifted to
the right. When off, text can be inserted in the line and old text will
automatically be replaced with the new text.
Return
Scrolls down to display the next line or used to issue a command.
Space
Scrolls down to display the next page.
ESC
Escapes from the displaying page.
Display Result Output Modifiers
Results displayed by show commands can be filtered using the following parameters:
begin FILTER-STRING - This parameter is used to start the display with the first line that
matches the filter string.
include FILTER-STRING - This parameter is used to display all the lines that match the filter
string.
exclude FILTER-STRING - This parameter is used to exclude the lines that match the filter
string from the display.
The example below shows how to use the begin FILTER-STRING parameter in a show command.
Page 11
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
8
Switch#show running-config | begin # AAA
# AAA
configure terminal
# AAA START
no aaa new-model
# AAA END
end
# PRIVMGMT
configure terminal
# COMMAND LEVEL START
# COMMAND LEVEL END
# LEVEL START
# LEVEL END
# ACCOUNT START
# ACCOUNT END
# LOGIN START
# LOGIN END
end
# CLI
# BASIC
CTRL+C ESC q Quit SPACE n Next Page ENTER Next Entry a All
The example below shows how to use the include FILTER-STRING parameter in a show command.
Switch#show running-config | include # DEVICE
# DEVICE
Switch#
The example below shows how to use the exclude FILTER-STRING parameter in a show command.
Page 12
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
9
Switch#show running-config | exclude # DEVICE
Building configuration...
Current configuration : 37933 bytes
#-------------------------------------------------------------------------------
# DGS-1510-28XMP Gigabit Ethernet SmartPro Switch
# Configuration
#
# Firmware: Build 1.30.003
# Copyright(C) 2015 D-Link Corporation. All rights reserved.
#-------------------------------------------------------------------------------
# STACK
end
end
configure terminal
end
# AAA
CTRL+C ESC q Quit SPACE n Next Page ENTER Next Entry a All
Page 13
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
10
2. Basic CLI Commands
2-1 help
This command is used to display a brief description of the help system. Use the help command in any
command mode.
help
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
The help command provides a brief description for the help system, which includes the following
functions:
To list all commands available for a particular command mode, enter a question mark (?) at
the system prompt.
To obtain a list of commands that begin with a particular character string, enter the
abbreviated command entry immediately followed by a question mark (?). This form of help is
called word help, because it lists only the keywords or arguments that begin with the
abbreviation entered.
To list the keywords and arguments associated with a command, enter a question mark (?) in
place of a keyword or argument on the command line. This form of help is called the
command syntax help, because it lists the keywords or arguments that apply based on the
command, keywords, and arguments already entered.
Example
This example shows how the help command is used to display a brief description of the help system.
Page 14
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
11
Switch#help
The switch CLI provides advanced help feature.
1. Help is available when you are ready to enter a command
argument (e.g. 'show ?') and want to know each possible
available options.
2. Help is provided when an abbreviated argument is entered
and you want to know what arguments match the input(e.g. 'show ve?'.).
If nothing matches, the help list will be empty and you must backup
until entering a '?' shows the available options.
3. For completing a partial command name could enter the abbreviated
command name immediately followed by a <Tab> key.
Note:
Since the character '?' is used for help purpose, to enter
the character '?' in a string argument, press ctrl+v immediately
followed by the character '?'.
Switch#
The following example shows how to use the word help to display all the Privileged EXEC Mode
commands that begin with the letters “re”. The letters entered before the question mark (?) are
reprinted on the next command line to allow the user to continue entering the command.
Switch#re?
reboot rename renew reset
Switch#re
The following example shows how to use the command syntax help to display the next argument of
a partially complete IP access-list standard command. The characters entered before the question
mark (?) is reprinted on the next command line to allow the user to continue entering the command.
Switch(config)#ip access-list standard ?
<1-1999> Standard IP access-list number
<cr>
Switch(config)#ip access-list standard
2-2 enable
This command is used to enter the Privileged EXEC Mode.
enable [PRIVILEGE-LEVEL]
Parameters
PRIVILEGE-LEVEL
(Optional) Specifies to set the privilege level for the user. The
privilege level is between 1 and 15. If not specified, level 15 will be
used.
Default
None.
Command Mode
Page 15
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
12
User EXEC Mode.
Privilege EXEC Mode.
Command Default Level
Level: 1.
Usage Guideline
Execute this command if the current level is lower than the command level. If the privileged level
requires a password, enter it in the field provided. However, only three attempts are allowed. Failure
to access this level returns the user to the current level.
Example
This example shows how to enter the Privileged EXEC Mode.
Switch# enable 15
password:***
Switch#
2-3 disable
This command is used to downgrade to a level lower user level than the privileged level.
disable [PRIVILEGE-LEVEL]
Parameters
PRIVILEGE LEVEL
Specifies the privilege level to enter. If not specified, level 1 is used.
Default
None.
Command Mode
User EXEC Mode.
Privilege EXEC Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to enter the privilege level, which is lower than the current level. When using this
command to enter the privilege level, that has a password configured, no password is needed.
Example
This example shows how to logout.
Switch# disable
Switch> logout
2-4 configure terminal
This command is used to enter the Global Configuration Mode.
configure terminal
Page 16
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
13
Parameters
None.
Default
None
Command Mode
Privilege EXEC Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to enter the Global Configuration Mode.
Example
This example shows how to enter into Global Configuration Mode.
Switch# configure terminal
Switch(config)#
2-5 login (EXEC)
This command is used to configure a login username.
login
Parameters
None.
Default
None.
Command Mode
User EXEC Mode.
Privileged EXEC Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to change the login account. Three attempts are allowed to login to the Switch’s
interface. When using Telnet, if all attempts fail, access will return to the command prompt. If no
information is entered within 60 seconds, the session will return to the state when logged out.
Example
This example shows how to login with username “user1”.
Switch# login
Username: user1
Password: xxxxx
Switch#
Page 17
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
14
2-6 login (Line)
This command is used to set the line login method. Use the no form of this command to disable the
login.
login [local]
no login
Parameters
login
Specifies that the line login method will be login.
local
Specifies that the line login method will be local.
Default
By default, all line interfaces use the login local method (by username and password).
Command Mode
Line Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
For Console and Telnet access, when AAA is enabled, the line uses rules configured by the AAA
module. When AAA is disabled, the line uses the following authentication rules:
When login is disabled, the user can enter the line at Level 1.
When the by password option is selected, after inputting the same password as the
command password, the user enter the line at level 1. If the password wasn’t previously
configured an error message will be displayed and the session will be closed.
When the username and password option is selected, enter the username and password
configured by the username command.
For SSH access, there are three authentication types:
SSH public key,
Host-based authentication, and
Password authentication.
The SSH public key and host-based authentication types are independent from the login command in
the line mode. If the authentication type is password, the following rules apply:
When AAA is enabled, the AAA module is used.
When AAA is disabled, the following rules are used:
o When login is disabled, the username and password is ignored. Enter the details at
Level 1.
o When the username and password option is selected, use the username and
password setup by the username command.
o When the password option is selected, the username is ignored but a password is
required using the password command to enter the line at level 1.
Example
This example shows how to enter the Line Configuration Mode and to create a password for the line
user. This password only takes effect once the corresponding line is set to login.
Switch# configure terminal
Switch(config)# line console
Switch(config-line)# password loginpassword
Switch(config-line)#
Page 18
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
15
This example shows how to configure the line console login method as “login”.
Switch# configure terminal
Switch(config)# line console
Switch(config-line)# login
Switch(config-line)#
This example shows how to enter the login command. The device will check the validity of the user
from the password create command. If correct, the user will have access at the particular level.
Switch#login
Password:*************
Switch#
This example shows how to create a username “useraccount” with the password of “pass123” and
use Privilege 12.
Switch# configure terminal
Switch(config)# username useraccount privilege 12 password 0 pass123
Switch(config)#
This example shows how to configure the login method as login local.
Switch# configure terminal
Switch(config)# line console
Switch(config-line)# login local
Switch(config-line)#
2-7 logout
This command is used to close an active terminal session by logging off the Switch.
logout
Parameters
None.
Default
None.
Command Mode
User EXEC Mode.
Privilege EXEC Mode.
Command Default Level
Level:1.
Usage Guideline
Use this command to close an active terminal session by logging out of the device.
Example
This example shows how to logout
Page 19
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
16
Switch# disable
Switch# logout
2-8 end
This command is used to end the current configuration mode and return to the highest mode in the
CLI mode hierarchy which is either the User EXEC Mode or the Privileged EXEC Mode.
end
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Executing this command will return access to the highest mode in the CLI hierarchy regardless of
what configuration mode or configuration sub-mode currently located at.
Example
This example shows how to end the Interface Configuration Mode and go back to the Privileged
EXEC Mode.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)#end
Switch#
2-9 exit
This command is used to end the configuration mode and go back to the last mode. If the current
mode is the User EXEC Mode or the Privilege EXEC Mode, executing the exit command logs you out
of the current session.
exit
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Page 20
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
17
Level: 1.
Usage Guideline
Use this command to exit the current configuration mode and go back to the last mode. When the
user is in the User EXEC Mode or the Privilege EXEC Mode, this command will logout the session.
Example
This example shows how to exit from the Interface Configuration Mode and return to the Global
Configuration Mode.
Switch# configure terminal
Switch(config) interface eth1/0/1
Switch(config-if)#exit
Switch(config)#
2-10 show history
This command is used to list the commands entered in the current EXEC Mode session.
show history
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Commands entered are recorded by the system. A recorded command can be recalled by pressing
CTRL+P or the Up Arrow key which will recall previous commands in sequence. The history buffer
size is fixed at 20 commands.
The function key instructions, below, displays how to navigate the command in the history buffer.
CTRL+P or the Up Arrow key - Recalls commands in the history buffer, beginning with the
most recent command. Repeat the key sequence to recall successively older commands.
CTRL+N or the Down Arrow key - Returns to more recent commands in the history buffer
after recalling commands with Ctrl-P or the Up Arrow key. Repeat the key sequence to recall
successively more recent commands.
Example
This example shows how to display the command buffer history.
Switch# show history
help
history
Switch#
Page 21
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
18
2-11 show environment
This command is used to display fan, temperature, power availability and status information.
show environment [fan | power | temperature]
Parameters
fan
(Optional) Specifies to display the Switch fan detailed status.
power
(Optional) Specifies to display the Switch power detailed status.
temperature
(Optional) Specifies to display the Switch temperature detailed
status.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
If the type is not specified, all types of environment information will be displayed.
Example
This example shows how to display fan, temperature, power availability and status information.
Switch#show environment
Detail Temperature Status:
Unit Temperature Descr/ID Current/Threshold Range
----- ------------------------------------------------------
1 Central Temperature/1 27C/11~79C
Status code: * temperature is out of threshold range
Detail Fan Status:
--------------------------------------------------------------
Right Fan 1 (OK) Right Fan 2 (OK)
Detail Power Status:
Unit Power Module Power Status
----- ---------------- -------------
1 Power 1 in-operation
Switch#
Display Parameters
Power status
in-operation: The power rectifier is in normal operation.
failed: The power rectifier not working normally.
empty: The power rectifier is not installed.
Page 22
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
19
2-12 show unit
This command is used to display information about system units.
show unit [UNIT-ID]
Parameters
UNIT-ID
(Optional) Specify the unit to display.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command displays information about the system modules. If no option is specified, then all of
units’ information will be displayed.
Example
This example shows how to display the information about units on a system.
Switch#show unit
Unit Model Descr Model Name
---- ------------------------------------------- ------------------
1 No module description DGS-1510-28P
Unit Serial-Number Status Up Time
---- --------------------------------- --------- -----------------
1 ok 0DT6H32M18S
Unit Memory Total Used Free
---- -------- ---------- ---------- ----------
1 DRAM 131072 K 66567 K 64505 K
1 FLASH 29937 K 7799 K 22138 K
Switch#
2-13 show cpu utilization
This command is used to display the CPU utilization information.
show cpu utilization
Parameters
None.
Default
None.
Page 23
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
20
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command displays the system’s CPU utilization information in 5 second, 1 minute, and 5 minute
intervals.
Example
This example shows how to display the information about CPU utilization.
Switch#show cpu utilization
CPU Utilization
Five seconds - 8 % One minute - 7 % Five minutes - 7 %
Switch#
2-14 show version
This command is used to display the Switch’s software version information.
show version
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command displays version information about the Switch.
Example
This example shows how to displays version information about the Switch.
Page 24
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
21
Switch#show version
System MAC Address: 3C-1E-04-A1-CC-00
Unit ID Module Name Versions
------- ------------------ ---------------------
1 DGS-1510-28XMP H/W:A1
Bootloader:1.00.012
Runtime:1.30.003
Switch#
2-15 snmp-server enable traps environment
This command is used to enable the power, temperature and fan trap state.
snmp-server enable traps environment [fan] [power] [temperature]
no snmp-server enable traps environment [fan] [power] [temperature]
Parameters
fan
(Optional) Specifies to enable the fan trap state for warning fan
event (fan failed or fan recover).
power
(Optional) Specifies to enable the power trap state for warning
power event (power failed or power recover).
temperature
(Optional) Specifies to enable the temperature trap state for warning
temperature event (temperature exceeds the thresholds or
temperature recover).
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to configure the environment temperature threshold which corresponds to the
normal range of the temperature defined for the sensor. The low threshold must be smaller than the
high threshold. The configured range must fall within the operational range which corresponds to the
minimum and maximum allowed temperatures defined for the sensor. When the configured threshold
is crossed, a notification will be sent.
Example
This example shows how to configure the environment temperature thresholds for thermal sensor ID 1
on unit 1.
Switch# configure terminal
Switch(config)# environment temperature threshold unit 1 thermal 1 high 100 low 20
Switch(config)#
Page 25
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
22
2-16 environment temperature threshold
This command is used to configure the environment temperature thresholds. Use the no form of this
command to revert to the default setting.
environment temperature threshold unit UNIT-ID thermal THREMAL-ID [high VALUE] [low
VALUE]
no environment temperature threshold unit UNIT-ID thermal THREMAL-ID [high] [low]
Parameters
unit UNIT-ID
Specifies the unit ID.
thermal THERMAL-ID
Specifies the thermal sensor’s ID.
high
(Optional) Specifies the high threshold of the temperature in
Celsius. The range is from -100 to 200.
low
(Optional) Specifies the low threshold of the temperature in Celsius.
The range is from -100 to 200. The low threshold must be smaller
than the high threshold.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to configure the environment temperature threshold which corresponds to the
normal range of the temperature defined for the sensor. The low threshold must be smaller than the
high threshold. The configured range must fall within the operational range which corresponds to the
minimum and maximum allowed temperatures defined for the sensor. When the configured threshold
is crossed, a notification will be sent.
Example
This example shows how to configure the environment temperature thresholds for thermal sensor ID 1
on unit 1.
Switch# configure terminal
Switch(config)# environment temperature threshold unit 1 thermal 1 high 100 low 20
Switch(config)#
2-17 privilege
This command is used to configure the execution rights of a command string to a privilege level. Use
the no form of this command to revert the command string to the default setting level.
privilege MODE {level PRIVILEGE-LEVEL | reset } COMMAND-STRING
no privilege MODE COMMAND-STRING
Parameters
MODE
Specifies the command mode of the command.
Page 26
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
23
level PRIVILEGE-LEVEL
Specifies the level of the execution right. The value is from 1 to 15.
reset
Specifies to revert the command to the default setting level.
COMMAND-STRING
Specifies the command to be changed.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
This command is used to configure the execution rights of a command string to a privilege level.
When this command is used, the command string used must exist at current command level. When
more than one command begins with the command string specified, all of the commands starting with
that command string will be changed to the specified command level.
Example
This example shows how to configure the configure terminal command string as a level 1 command.
Switch#configure terminal
Switch(config)#privilege exec level 1 configure terminal
Switch(config)#
2-18 show privilege
This command is used to display current privilege level.
show privilege
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command is used to display current privilege level.
Example
This example shows how to display the current privilege level.
Switch# Switch#show privilege
Current privilege level is 15
Switch#
Page 27
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
24
Page 28
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
25
3. 802.1X Commands
3-1 clear dot1x counters
This command is used to clear 802.1X counters (diagnostics, statistics and session statistics).
clear dot1x counters {all | interface INTERFACE-ID [, | -]}
Parameters
all
Specifies to clear 802.1X counters (diagnostics, statistics and
session statistics) on all interfaces.
interface INTERFACE-ID
Specifies to clear 802.1X counters (diagnostics, statistics and
session statistics) on the specified interface. Valid interfaces are
physical ports (including type, stack member, and port number).
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
Default
None.
Command Mode
Privileged EXEC Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to clear 802.1X counters (diagnostics, statistics and session statistics).
Example
This example shows how to clear 802.1X counters (diagnostics, statistics and session statistics) on
the Ethernet port 1/0/1.
Switch# clear dot1x counters interface eth1/0/1
Switch#
3-2 dot1x control-direction
This command is used to configure the direction of the traffic on a controlled port as unidirectional (in)
or bidirectional (both). Use the no form of this command to revert to the default setting.
dot1x control-direction {both | in}
no dot1x control-direction
Parameters
both
Specifies to enable bidirectional control for the port.
in
Specifies to enable in direction control for the port.
Page 29
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
26
Default
By default, this option is bidirectional mode.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is only available for physical port interface configuration. If the port control is set to
force-authorized, then the port is not controlled in both directions. If the port control is set to auto,
then the access to the port for the controlled direction needs to be authenticated. If the port control is
set to force-unauthorized, then the access to the port for the controlled direction is blocked.
Suppose that port control is set to auto. If the control direction is set to both, then the port can receive
and transmit EAPOL packets only. All user traffic is blocked before authentication. If the control
direction is set to in, then in addition to receiving and transmitting EAPOL packets, the port can
transmit user traffic but not receive user traffic before authentication.
Example
This example shows how to configure the controlled direction of the traffic through Ethernet eth1/0/1
as unidirectional.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x control-direction in
Switch(config-if)#
3-3 dot1x default
This command is used to reset the IEEE 802.1X parameters on a specific port to their default settings.
dot1x default
Parameters
None.
Default
IEEE 802.1X authentication is disabled.
Control direction is bidirectional (both).
Port control is auto.
Forward PDU on port is disabled.
Maximum request is 2 times.
Server timer is 30 seconds.
Supplicant timer is 30 seconds.
Transmit interval is 30 seconds.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Page 30

DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
27
This command is used to reset all the IEEE 802.1X parameters on a specific port to their default
settings.
Example
This example shows how to reset the 802.1X parameters on port 1/0/1.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x default
Switch(config-if)#
3-4 dot1x port-control
This command is used to control the authorization state of a port. Use the no form of this command to
revert to the default setting.
dot1x port-control {auto | force-authorized | force-unauthorized}
no dot1x port-control
Parameters
auto
Specifies to enable IEEE 802.1X authentication for the port.
force-authorized
Specifies the port to the force authorized state.
force-unauthorized
Specifies the port to the force unauthorized state.
Default
By default, this option is set as auto.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command takes effect only when IEEE 802.1X PAE authenticator is globally enabled by the
dot1x system-auth-control command and is enabled for a specific port by using the dot1x PAE
authenticator.
This command is only available for physical port interface configuration.
If the port control is set to force-authorized, then the port is not controlled in both directions. If the
port control is set to auto, then the access to the port for the controlled direction needs to be
authenticated. If the port control is set to force-unauthorized, then the access to the port for the
controlled direction is blocked.
Example
This example shows how to deny all access on Ethernet port 1/0/1.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x port-control force-unauthorized
Switch(config-if)#
Page 31
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
28
3-5 dot1x forward-pdu
This command is used to enable the forwarding of the dot1x PDU. Use the no form of this command
to disable the forwarding of the dot1x PDU.
dot1x forward-pdu
no dot1x forward-pdu
Parameters
None.
Default
By default, this option is disabled.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is only available for physical port interface configuration. This command only takes
effect when the dot1x authentication function is disabled on the receipt port. The received PDU will be
forwarded in either the tagged or untagged form based on the VLAN setting.
Example
This example shows how to configure the forwarding of the dot1x PDU.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x forward-pdu
Switch(config-if)#
3-6 dot1x initialize
This command is used to initialize the authenticator state machine on a specific port or associated
with a specific MAC address.
dot1x initialize {interface INTERFACE-ID [, | -] | mac-address MAC-ADDRESS}
Parameters
interface INTERFACE-ID
Specifies the port on which the authenticator state machine will be
initialized. Valid interfaces are physical ports.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
mac-address MAC-ADDRESS
Specifies the MAC address to be initialized.
Default
None.
Page 32
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
29
Command Mode
Privileged EXEC Mode.
Command Default Level
Level: 12.
Usage Guideline
Under the multi-host mode, specify an interface ID to initialize a specific port.
Under the multi-auth mode, specify a MAC address to initialize a specific MAC address.
Example
This example shows how to initialize the authenticator state machine on Ethernet port 1/0/1.
Switch# dot1x initialize interface eth1/0/1
Switch#
3-7 dot1x max-req
This command is used to configure the maximum number of times that the backend authentication
state machine will retransmit an Extensible Authentication Protocol (EAP) request frame to the
supplicant before restarting the authentication process Use the no form of this command to revert to
the default setting.
dot1x max-req TIMES
no dot1x max-req
Parameters
TIMES
Specifies the number of times that the Switch retransmits an EAP
frame to the supplicant before restarting the authentication process.
The range is 1 to 10.
Default
By default, this value is 2.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The command is only available for physical port interface configuration. If no response to an
authentication request from the supplicant within the timeout period (specified by the dot1x timeout
tx-period SECONDS command) the Switch will retransmit the request. This command is used to
specify the number of retransmissions.
Example
This example shows how to configure the maximum number of retries on Ethernet port 1/0/1 to be 3.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x max-req 3
Switch(config-if)#
Page 33
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
30
3-8 dot1x pae authenticator
This command is used to configure a specific port as an IEEE 802.1X port access entity (PAE)
authenticator. Use the no form of this command to disable the port as an IEEE 802.1X authenticator.
dot1x pae authenticator
no dot1x pae authenticator
Parameters
None.
Default
By default, this option is disabled.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is only available for physical port interface configuration. Globally enable IEEE 802.1X
authentication on the Switch by using the dot1x system-auth-control command. When IEEE 802.1X
authentication is enabled, the system will authenticate the 802.1X user based on the method list
configured by the aaa authentication dot1x default command.
Example
This example shows how to configure Ethernet port 1/0/1 as an IEEE 802.1X PAE authenticator.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x pae authenticator
Switch(config-if)#
This example shows how to disable IEEE 802.1X authentication on Ethernet port 1/0/1.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# no dot1x pae authenticator
Switch(config-if)#
3-9 dot1x re-authenticate
This command is used to re-authenticate a specific port or a specific MAC address.
dot1x re-authenticate {interface INTERFACE-ID [, | -] | mac-address MAC-ADDRESS}
Parameters
interface INTERFACE-ID
Specifies the port to re-authenticate. Valid interfaces are physical
ports.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
Page 34
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
31
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
mac-address MAC-ADDRESS
Specifies the MAC address to re-authenticate.
Default
None.
Command Mode
Privileged EXEC Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to re-authenticate a specific port or a specific MAC address.
Example
This example shows how to re-authenticate Ethernet port 1/0/1.
Switch# dot1x re-authenticate interface eth1/0/1
Switch#
3-10 dot1x system-auth-control
This command is used to globally enable IEEE 802.1X authentication on a switch. Use the no form of
this command to disable IEEE 802.1X authentication function.
dot1x system-auth-control
no dot1x system-auth-control
Parameters
None.
Default
By default, this option is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The 802.1X authentication function restricts unauthorized hosts from accessing the network. Use the
dot1x system-auth-control command to globally enable the 802.1X authentication control. When
802.1X authentication is enabled, the system will authenticate the 802.1X user based on the method
list configured by the aaa authentication dot1x default command.
Example
This example shows how to enable IEEE 802.1X authentication globally on a switch.
Switch# configure terminal
Switch(config)# dot1x system-auth-control
Switch(config)#
Page 35
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
32
3-11 dot1x timeout
This command is used to configure IEEE 802.1X timers. Use the no form of this command to revert a
specific timer setting to the default setting.
dot1x timeout {server-timeout SECONDS | supp-timeout SECONDS | tx-period SECONDS}
no dot1x timeout {server-timeout | supp-timeout | tx-period}
Parameters
server-timeout SECONDS
Specifies the number of seconds that the Switch will wait for the
request from the authentication server before timing out the server.
On timeout, authenticator will send EAP-Request packet to client.
The range is 1 to 65535.
supp-timeout SECONDS
Specifies the number of seconds that the Switch will wait for the
response from the supplicant before timing out the supplicant
messages other than EAP request ID. The range is 1 to 65535
tx-period SECONDS
Specifies the number of seconds that the Switch will wait for a
response to an EAP-Request/Identity frame from the supplicant
before retransmitting the request. The range is 1 to 65535
Default
The server-timeout is 30 seconds.
The supp-timeout is 30 seconds.
The tx-period is 30 seconds.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is only available for physical port interface configuration.
Example
This example shows how to configure the server timeout value, supplicant timeout value, and the TX
period on Ethernet port 1/0/1 to be 15, 15, and 10 seconds, respectively.
Switch# configure terminal
Switch(config)# interface eth1/0/1
Switch(config-if)# dot1x timeout server-timeout 15
Switch(config-if)# dot1x timeout supp-timeout 15
Switch(config-if)# dot1x timeout tx-period 10
Switch(config-if)#
3-12 show dot1x
This command is used to display the IEEE 802.1X global configuration or interface configuration.
show dot1x [interface INTERFACE-ID [, | -]]
Parameters
Page 36
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
33
interface INTERFACE-ID
(Optional) Specifies to display the dot1x configuration on the
specified interface or range of interfaces. If not specified, the global
configuration will be displayed.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command can be used to display the global configuration or interface configuration. If the
configuration command is entered without parameters, the global configuration will be displayed.
Otherwise, the configuration on the specified interface will be displayed.
Example
This example shows how to display the dot1X global configuration.
Switch# show dot1x
802.1X : Enabled
Trap State : Enabled
Switch#
This example shows how to display the dot1X configuration on Ethernet port 1/0/1.
Switch# show dot1x interface eth1/0/1
Interface : eth1/0/1
PAE : Authenticator
Control Direction : Both
Port Control : Auto
Tx Period : 30 sec
Supp Timeout : 30 sec
Server Timeout : 30 sec
Max-req : 2 times
Forward PDU : Disabled
Switch#
3-13 show dot1x diagnostics
This command is used to display IEEE 802.1X diagnostics. If no interface is specified, information
about all interfaces will be displayed.
show dot1x diagnostics [interface INTERFACE-ID [, | -]]
Page 37
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
34
Parameters
interface INTERFACE-ID
(Optional) Specifies to display the dot1x diagnostics on the
specified interface or range of interfaces. If not specified,
information about all interfaces will be displayed.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command can be used to display 802.1X diagnostics. Using this command without parameters
will display information about all interfaces. Otherwise, the diagnostics on the specified interface will
be displayed.
Example
This example shows how to display the dot1X diagnostics on Ethernet port 1/0/1.
Switch# show dot1x diagnostics interface eth1/0/1
eth1/0/1 dot1x diagnostic information are following:
EntersConnecting : 20
EAP-LogoffsWhileConnecting : 0
EntersAuthenticating : 0
SuccessesWhileAuthenticating : 0
TimeoutsWhileAuthenticating : 0
FailsWhileAuthenticating : 0
ReauthsWhileAuthenticating : 0
EAP-StartsWhileAuthenticating : 0
EAP-LogoffsWhileAuthenticating : 0
ReauthsWhileAuthenticated : 0
EAP-StartsWhileAuthenticated : 0
EAP-LogoffsWhileAuthenticated : 0
BackendResponses : 0
BackendAccessChallenges : 0
BackendOtherRequestsToSupplicant : 0
BackendNonNakResponsesFromSupplicant : 0
BackendAuthSuccesses : 0
BackendAuthFails : 0
Switch#
3-14 show dot1x statistics
This command is used to display IEEE 802.1X statistics. If no interface is specified, information about
all interfaces will be displayed.
Page 38
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
35
show dot1x statistics [interface INTERFACE-ID [, | -]]
Parameters
interface INTERFACE-ID
(Optional) Specifies to display the dot1x diagnostics on the
specified interface or range of interfaces. If not specified,
information about all interfaces will be displayed.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command can be used to display 802.1X statistics. Using this command without parameters will
display information about all interfaces. Otherwise, the statistics on the specified interface will be
displayed.
Example
This example shows how to display dot1X statistics on Ethernet port 1/0/1.
Switch# show dot1x statistics interface eth1/0/1
eth1/0/1 dot1x statistics information:
EAPOL Frames RX : 1
EAPOL Frames TX : 4
EAPOL-Start Frames RX : 0
EAPOL-Req/Id Frames TX : 6
EAPOL-Logoff Frames RX : 0
EAPOL-Req Frames TX : 0
EAPOL-Resp/Id Frames RX : 0
EAPOL-Resp Frames RX : 0
Invalid EAPOL Frames RX : 0
EAP-Length Error Frames RX : 0
Last EAPOL Frame Version : 0
Last EAPOL Frame Source : 00-10-28-00-19-78
Switch#
3-15 show dot1x session-statistics
This command is used to display IEEE 802.1X session statistics. If no interface specified, information
about all interfaces will be displayed.
show dot1x session-statistics [interface INTERFACE-ID [, | -]]
Page 39
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
36
Parameters
interface INTERFACE-ID
(Optional) Specifies to display the dot1x diagnostics on the
specified interface or range of interfaces. If not specified,
information about all interfaces will be displayed.
,
(Optional) Specifies a series of interfaces, or separate a range of
interfaces from a previous range. No space is allowed before and
after the comma.
-
(Optional) Specifies a range of interfaces. No space is allowed
before and after the hyphen.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command can be used to display 802.1X session statistics. Using this command without
parameters will display information about all interfaces. Otherwise, the session statistics on the
specified interface will be displayed.
Example
This example shows how to display dot1X session statistics on Ethernet port 1/0/1.
Switch# show dot1x session-statistics interface eth1/0/1
eth6/0/1 session statistic counters are following:
SessionOctetsRX : 0
SessionOctetsTX : 0
SessionFramesRX : 0
SessionFramesTX : 0
SessionId :
SessionAuthenticationMethod : Remote Authentication Server
SessionTime : 0
SessionTerminateCause :SupplicantLogoff
SessionUserName :
Switch#
3-16 snmp-server enable traps dot1x
This command is used to enable sending SNMP notifications for 802.1X authentication. Use the no
form of this command to disable sending SNMP notifications.
snmp-server enable traps dot1x
no snmp-server enable traps dot1x
Parameters
None.
Default
Page 40
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
37
By default, this option is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command can be used to enable or disable sending SNMP notifications for 802.1X
authentication.
Example
This example shows how to enable sending trap for 802.1X authentication.
Switch# configure terminal
Switch(config)#snmp-server enable traps dot1x
Switch(config)#
Page 41
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
38
4. Access Control List (ACL) Commands
4-1 access-list resequence
This command is used to re-sequence the sequence number of the access list entries in an access
list. Use the no form of this command to revert to the default settings.
access-list resequence {NAME | NUMBER} STARTING-SEQUENCE-NUMBER INCREMENT
no access-list resequence
Parameters
NAME
Specifies the name of the access list to be configured. It can be a
maximum of 32 characters.
NUMBER
Specifies the number of the access list to be configured.
STARTING-SEQUENCENUMBER
Specifies that the access list entries will be re-sequenced using this
initial value. The default value is 10. The range of possible
sequence numbers is 1 through 65535.
INCREMENT
Specifies the number that the sequence numbers step. The default
value is 10. For example, if the increment (step) value is 5 and the
beginning sequence number is 20, the subsequent sequence
numbers are 25, 30, 35, 40, and so on. The range of valid values is
from 1 to 32.
Default
The default start sequence number is 10.
The default increment is 10.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This feature allows the user to re-sequence the entries of a specified access list with an initial
sequence number determined by the STARTING-SEQUENCE-NUMBER parameter and continuing in
the increments determined by the INCREMENT parameter. If the highest sequence number exceeds
the maximum possible sequence number, then there will be no re-sequencing.
If a rule entry is created without specifying the sequence number, the sequence number will be
automatically assigned. If it is the first entry, a start sequence number is assigned. Subsequent rule
entries are assigned a sequence number that is increment value greater than the largest sequence
number in that access list and the entry is placed at the end of the list.
After the start sequence number or increment change, the sequence number of all previous rules
(include the rules that assigned sequence by user) will change according to the new sequence setting.
Example
This example shows how to re-sequence the sequence number of an IP access-list, named R&D.
Page 42
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
39
Switch# configure terminal
Switch(config)# show access-list ip R&D
Extended IP access list R&D(ID: 3552)
10 permit tcp any 10.20.0.0 255.255.0.0
20 permit tcp any host 10.100.1.2
30 permit icmp any any
Switch(config)# ip extended access-list R&D
Switch(config-ip-ext-acl)# 5 permit tcp any 10.30.0.0 255.255.0.0
Switch(config-ip-ext-acl)# exit
Switch(config)# show access-list ip R&D
Extended IP access list R&D(ID: 3552)5 permit tcp any 10.30.0.0 255.255.0.0
10 permit tcp any 10.20.0.0 255.255.0.0
20 permit tcp any host 10.100.1.2
30 permit icmp any any
Switch(config)# access-list resequence R&D 1 2
Switch(config)# show access-list ip R&D
Extended IP access list R&D(ID: 3552)
1 permit tcp any 10.30.0.0 255.255.0.0
3 permit tcp any 10.20.0.0 255.255.0.0
5 permit tcp any host 10.100.1.2
7 permit icmp any any
Switch(config)#
4-2 acl-hardware-counter
This command is used to enable the ACL hardware counter of the specified access-list name for
access group functions or access map for the VLAN filter function. Use the no form of this command
to disable the ACL hardware counter function.
acl-hardware-counter {access-group {ACCESS-LIST-NAME | ACCESS-LIST-NUMBER} | vlan-
filter ACCESS-MAP-NAME}
no acl-hardware-counter {access-group {ACCESS-LIST-NAME | ACCESS-LIST-NUMBER} |
vlan-filter ACCESS-MAP-NAME}
Parameters
access-group ACCESS-LIST-
NAME
Specifies the name of the access list to be configured.
access-group ACCESS-LISTNUMBER
Specifies the number of the access list to be configured.
vlan-filter ACCESS-MAPNAME
Specifies the name of the access map to be configured.
Default
By default, this option is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Page 43
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
40
The command with parameter access-group will enable the ACL hardware counter for all ports that
have applied the specified access-list name or number. The number of packets, that match each rule,
are counted.
The command with parameter vlan-filter will enable the ACL hardware counter for all VLAN(s) that
have applied the specified VLAN access-map. The number of packets that permitted by each access
map are counted.
Example
This example shows how to enable the ACL hardware counter.
Switch# configure terminal
Switch(config)# acl-hardware-counter access-group abc
Switch(config)#
4-3 action
This command is used to configure the forward, drop, or redirect action of the sub-map in the VLAN
access-map sub-map configuration mode. Use the no form of this command to revert to the default
setting.
action {forward | drop | redirect INTERFACE-ID}
no action
Parameters
forward
Specifies to forward the packet when matched.
drop
Specifies to drop the packet when matched.
redirect INTERFACE-ID
Specifies the interface ID for the redirection action. Only physical
ports are allowed to be specified.
Default
By default, the action is forward.
Command Mode
VLAN Access-map Sub-map Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
One sub-map has only one action. The action configured later overwrites the previous action. A VLAN
access map can contain multiple sub-maps. The packet that matches a sub-map (a packet permitted
by the associated access-list) will take the action specified for the sub-map. No further checking
against the next sub-maps is done. If the packet does not match a sub-map, then the next sub-map
will be checked.
Example
This example shows how to configure the action in the sub-map.
Page 44
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
41
Switch# show vlan access-map
VLAN access-map vlan-map 20
match mac address: ext_mac(ID: 6856)
action: forward
Switch# configure terminal
Switch(config)# vlan access-map vlan-map 20
Switch(config-access-map)# action redirect eth1/0/5
Switch(config-access-map)# end
Switch# show vlan access-map
VLAN access-map vlan-map 20
match mac address: ext_mac(ID: 6856)
action: redirect eth1/0/5
Switch#
4-4 clear acl-hardware-counter
This command is used to clear the ACL hardware counter.
clear acl-hardware-counter {access-group [ACCESS-LIST-NAME | ACCESS-LIST-NUMBER] |
vlan-filter [ACCESS-MAP-NAME]}
Parameters
access-group ACCESS-LIST-
NAME
Specifies the name of the access list to be cleared.
access-group ACCESS-LISTNUMBER
Specifies the number of the access list to be configured.
vlan-filter ACCESS-MAPNAME
Specifies the name of the access map to be cleared.
Default
None.
Command Mode
Privileged EXEC Mode.
Command Default Level
Level: 12.
Usage Guideline
If no access-list name or number is specified with the parameter access-group, all access-group
hardware counters will be cleared. If no access-map name is specified with the parameter vlan-filter,
all VLAN filter hardware counters will be cleared.
Example
This example shows how to clear the ACL hardware counter.
Switch(config)# clear acl-hardware-counter access-group abc
Switch#
4-5 expert access-group
This command is used to apply a specific expert ACL to an interface. Use the no form of this
command to cancel the application.
Page 45
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
42
expert access-group {NAME | NUMBER} [in]
no expert access-group [NAME | NUMBER] [in]
Parameters
NAME
Specifies the name of the expert access-list to be configured. The
name can be up to 32 characters.
NUMBER
Specifies the number of the expert access list to be configured.
in
(Optional) Specifies to filter the incoming packets of the interface. If
the direction is not specified, in is used.
Default
None.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
If expert access group is already configured on the interface, the command applied later will overwrite
the previous setting. Only one access-list of the same type can be applied to the same interface; but
access-lists of different types can be applied to the same interface.
Example
This example shows how to apply an expert ACL to an interface. The purpose is to apply the ACL
“exp_acl” on the Ethernet port 1/0/2 to filter the incoming packets.
Switch# configure terminal
Switch(config)# interface eth1/0/2
Switch(config-if)# expert access-group exp_acl in
Switch(config-if)# end
Switch# show access-group interface eth1/0/2
eth1/0/2:
Inbound expert access-list : exp_acl(ID: 8999)
Switch#
4-6 expert access-list
This command is used to create or modify an extended expert ACL. This command will enter into the
extended expert access-list configuration mode. Use the no form of this command to remove an
extended expert access-list.
expert access-list extended NAME [NUMBER]
no expert access-list extended {NAME | NUMBER}
Parameters
NAME
Specifies the name of the extended expert access-list to be
configured. The name can be up to 32 characters.
NUMBER
Specifies the ID number of expert access list. For extended expert
access lists, the value is from 8000 to 9999.
Page 46
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
43
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The name must be unique among all access lists. The characters used in the name are case sensitive.
If the access list number is not specified, the biggest unused number in the range of the expert
access list numbers will be assigned automatically.
Example
This example shows how to create an extended expert ACL.
Switch# configure terminal
Switch(config)# expert access-list extended exp_acl
Switch(config-exp-nacl)# end
Switch# show access-list
Access-List-Name Type
-------------------------------------- ---------------
exp_acl(ID: 8999) expert ext-acl
Total Entries: 1
Switch#
4-7 ip access-group
This command is used to specify the IP access list to be applied to an interface. Use the no form of
this command to remove an IP access list.
ip access-group {NAME | NUMBER} [in]
no ip access-group [NAME | NUMBER] [in]
Parameters
NAME
Specifies the name of the IP access list to be applied. The
maximum length is 32 characters.
NUMBER
Specifies the number of the IP access list to be applied.
in
(Optional) Specifies that the IP access list will be applied to check
packets in the ingress direction. If the direction is not specified, in is
used.
Default
None.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Page 47
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
44
If an IP access group is already configured on the interface, the command applied later will overwrite
the previous setting. Only one access list of the same type can be applied to the same interface; but
access-lists of different types can be applied to the same interface.
The association of an access group with an interface will consume the filtering entry resource in the
switch controller. If the resources are insufficient to commit the command, then an error message will
be displayed. There is a limitation on the number of port operator resources. If applying the command
exhausts the available port selectors, then an error message will be displayed.
Example
This example shows how to specify the IP access list “Strict-Control” as an IP access group for an
Ethernet port 6/0/2.
Switch# configure terminal
Switch(config)# interface eth6/0/2
Switch(config-if)#ip access-group Strict-Control
The remaining applicable IP related access entries are 526
Switch(config-if)#
4-8 ip access-list
This command is used to create or modify an IP access list. This command will enter into the IP
access list configuration mode. Use the no form of this command to remove an IP access list.
ip access-list [extended] NAME [NUMBER]
no ip access-list [extended] {NAME | NUMBER}
Parameters
extended
(Optional) Specifies that without this option the IP access list is a
standard IP access list. When using the extended option, more
fields can be chosen for the filter.
NAME
Specifies the name of the IP access list to be configured. The
maximum length is 32 characters. The first character must be a
letter.
NUMBER
Specifies the ID number of the IP access list. For standard IP
access lists, this value is from 1 to 1999. For extended IP access
lists, this value is from 2000 to 3999.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The name must be unique among all access lists. The characters used in the name are case sensitive.
If the access list number is not specified, the biggest unused number in the range of IP access list
numbers will be assigned automatically.
Example
This example shows how to configure an extended IP access list, named “Strict-Control” and an IP
access-list, named “pim-srcfilter”.
Page 48
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
45
Switch# configure terminal
Switch(config)# ip access-list extended Strict-Control
Swtich(config-ip-ext-acl)# permit tcp any 10.20.0.0 255.255.0.0
Swtich(config-ip-ext-acl)# exit
Swtich(config)# ip access-list pim-srcfilter
Switch(config-ip-acl)# permit host 172.16.65.193 any
Switch(config-ip-acl)#
4-9 ipv6 access-group
This command is used to specify the IPv6 access list to be applied to an interface. Use the no form of
this command to remove an IPv6 access list.
ipv6 access-group {NAME | NUMBER} [in]
no ipv6 access-group [NAME | NUMBER] [in]
Parameters
NAME
Specifies the name of the IPv6 access list to be applied.
NUMBER
Specifies the number of the IPv6 access list to be applied.
in
(Optional) Specifies that the IPv6 access list will be applied to check
in the ingress direction. If the direction is not specified, in is used.
Default
None.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Only one access list of the same type can be applied to the same interface; but access lists of
different types can be applied to the same interface. The association of an access group with an
interface will consume the filtering entry resource in the switch controller. If the resource is insufficient
to commit the command, then an error message will be displayed.
There is a limitation on the number of port operator resources. If applying the command exhausts the
available port selectors, then an error message will be displayed.
Example
This example shows how to specify the IPv6 access list “ip6-control” as an IP access group for
eth3/0/3.
Switch# configure terminal
Switch(config)# interface eth3/0/3
Switch(config-if)# ipv6 access-group ip6-control in
The remaining applicable IPv6 related access entries are 156
Switch(config-if)#
4-10 ipv6 access-list
This command is used to create or modify an IPv6 access list. This command will enter into IPv6
access-list configuration mode. Use the no form of this command to remove an IPv6 access list.
Page 49
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
46
ipv6 access-list [extended] NAME [NUMBER]
no ipv6 access-list [extended] {NAME | NUMBER}
Parameters
extended
(Optional) Specifies that without this option the IPv6 access list is a
standard IPv6 access list. When using the extended option, the IPv6
access list is an extended IPv6 access list and more fields can be
chosen for the filter.
NAME
Specifies the name of the IPv6 access list to be configured. The
maximum length is 32 characters.
NUMBER
Specifies the ID number of the IPv6 access list. For standard IPv6
access lists, this value is from 11000 to 12999. For extended IPv6
access lists, this value is from 13000 to 14999.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The name must be unique among all access lists. The characters used in the name are case sensitive.
If the access list number is not specified, the biggest unused number in the range of the IPv6 access
list numbers will be assigned automatically.
Example
This example shows how to configure an IPv6 extended access list, named ip6-control.
Switch# configure terminal
Switch(config)# ipv6 access-list extended ip6-control
Swtich(config-ipv6-ext-acl)# permit tcp any 2002:f03::1/16
Switch(config-ipv6-ext-acl)#
This example shows how to configure an IPv6 standard access list, named ip6-std-control.
Switch# configure terminal
Switch(config)# ipv6 access-list ip6-std-control
Swtich(config-ipv6-acl)# permit any fe80::101:1/54
Switch(config-ipv6-acl)#
4-11 list-remark
This command is used to add remarks for the specified ACL. Use the no form of this command to
delete the remarks.
list-remark TEXT
no list-remark
Parameters
Page 50
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
47
TEXT
Specifies the remark information. The information can be up to 256
characters long.
Default
None.
Command Mode
Access-list Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is available in the MAC, IP, IPv6, and Expert Access-list Configure mode.
Example
This example shows how to add a remark to the access-list.
Switch# configure terminal
Switch(config)# ip extended access-list R&D
Switch(config-ip-ext-acl)# list-remark This access-list is used to match any IP
packets from the host 10.2.2.1.
Switch(config-ip-ext-acl)# end
Switch# show access-list ip
Extended IP access list R&D(ID: 3999)
10 permit host 10.2.2.1 any
This access-list is used to match any IP packets from the host 10.2.2.1.
Switch#
4-12 mac access-group
This command is used to specify a MAC access list to be applied to an interface. Use the no form of
this command to remove the access group control from the interface.
mac access-group {NAME | NUMBER} [in]
no mac access-group [NAME | NUMBER] [in]
Parameters
NAME
Specifies the name of the MAC access list to be applied.
NUMBER
Specifies the number of the MAC access list to be applied.
in
(Optional) Specifies that the MAC access list will be applied to
check in the ingress direction. If direction is not specified, in is used.
Default
None.
Command Mode
Interface Configuration Mode.
Command Default Level
Level: 12.
Page 51
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
48
Usage Guideline
If MAC access group is already configured on the interface, the command applied later will overwrite
the previous setting. MAC access-groups will only check non-IP packets.
Only one access list of the same type can be applied to the same interface; but access lists of
different types can be applied to the same interface.
The association of an access group with an interface will consume the filtering entry resource in the
switch controller. If the resource is insufficient to commit the command, then an error message will be
displayed.
Example
This example shows how to apply the MAC access list daily-profile to Ethernet port 5/0/1.
Switch# configure terminal
Switch(config)# interface eth5/0/1
Switch(config-if)# mac access-group daily-profile in
The remaining applicable MAC access entries are 204
Switch(config-if)#
4-13 mac access-list
This command is used to create or modify an MAC access list and this command will enter the MAC
access list configuration mode. Use the no form of this command to delete a MAC access list.
mac access-list extended NAME [NUMBER]
no mac access-list extended {NAME | NUMBER}
Parameters
NAME
Specifies the name of the MAC access-list to be configured. The
maximum length is 32 characters.
NUMBER
Specifies the ID number of the MAC access list, For extended MAC
access lists, this value is from 6000 to 7999.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to enter the MAC access-list configuration mode and use the permit or deny
command to specify the entries. The name must be unique among all access lists. The characters of
the name are case sensitive. If the access list number is not specified, the biggest unused number in
the range of the MAC access list numbers will be assigned automatically.
Example
This example shows how to enter the MAC access list configuration mode for a MAC access list
named “daily profile”.
Switch# configure terminal
Switch(config)# mac access-list extended daily-profile
Switch(config-mac-ext-acl)#
Page 52
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
49
4-14 match ip address
This command is used to associate an IP access list for the configured sub-map. The no form of this
command removes the match entry.
match ip address {ACL-NAME | ACL-NUMBER}
no match ip address
Parameters
ACL-NAME
Specifies the name of the ACL access list to be configured. The
name can be up to 32 characters.
ACL-NUMBER
Specifies the number of the IP ACL access list to be configured.
Default
None.
Command Mode
VLAN Access-map Sub-map Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to associate an IP access list with the configured sub-map. One sub-map can only
be associated with one access list (IP access list, IPv6 access list or MAC access list). IP sub-map
just checks IP packets. The newer command overwrites the previous setting.
Example
This example shows how to configure the match content in the sub-map.
Switch# configure terminal
Switch(config)# vlan access-map vlan-map 20
Switch(config-access-map)# match ip address sp1
Switch(config-access-map)#
4-15 match ipv6 address
This command is used to associate IPv6 access lists for the configured sub-maps. The no form of this
command removes the match entry.
match ipv6 address {ACL-NAME | ACL-NUMBER}
no match ipv6 address
Parameters
ACL-NAME
Specifies the name of the IPv6 ACL access list to be configured.
The name can be up to 32 characters.
ACL-NUMBER
Specifies the number of the IPv6 ACL access list to be configured.
Default
None.
Page 53
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
50
Command Mode
VLAN Access-map Sub-map Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to associate an IPv6 access list with the configured sub-map. One sub-map can
only be associated with one access list (IP access list, IPv6 access list or MAC access list). IPv6 submap just checks IPv6 packets. The later command overwrites the previous setting.
Example
This example shows how to set the match content in the sub-map.
Switch# configure terminal
Switch(config)# vlan access-map vlan-map 20
Switch(config-access-map)# match ipv6 address sp1
Switch(config-access-map)#
4-16 match mac address
This command is used to associate MAC access lists for the configured sub-maps. The no form of
this command removes the match entry.
match mac address {ACL-NAME | ACL-NUMBER}
no match mac address
Parameters
ACL-NAME
Specifies the name of the ACL MAC access list to be configured.
The name can be up to 32 characters.
ACL-NUMBER
Specifies the number of the ACL MAC access list to be configured.
Default
None.
Command Mode
VLAN Access-map Sub-map Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to associate a MAC access list with the configured sub-map. One sub-map can
only be associated with one access list (IP access list, IPv6 access list or MAC access list). MAC submap just check non-IP packets. The later command overwrites the previous setting.
Example
This example shows how to set the match content in the sub-map.
Switch# configure terminal
Switch(config)# vlan access-map vlan-map 30
Switch(config-access-map)# match mac address ext_mac
Switch(config-access-map)#
Page 54
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
51
4-17 permit | deny (expert access-list)
This command is used to add a permit or deny entry. Use the no form of this command to remove an
entry.
Extended Expert ACL:
[SEQUENCE-NUMBER] {permit | deny} PROTOCOL {SRC-IP-ADDR SRC-IP-WILDCARD | host
SRC-IP-ADDR | any} {SRC-MAC-ADDR SRC-MAC-WILDCARD | host SRC-MAC-ADDR | any}
{DST-IP-ADDR DST-IP-WILDCARD | host DST-IP-ADDR | any} {DST-MAC-ADDR DST-MAC-
WILDCARD | host DST-MAC-ADDR | any} [cos OTER-COS] [vlan OUTER-VLAN] [fragments]
[[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} tcp {SRC-IP-ADDR SRC-IP-WILDCARD | host SRC-IP-
ADDR | any} {SRC-MAC-ADDR SRC-MAC-WILDCARD | host SRC-MAC-ADDR | any} [{eq | lt |
gt | neq} PORT | range MIN-PORT MAX-PORT] {DST-IP-ADDR DST-IP-WILDCARD | host DST-
IP-ADDR | any} {DST-MAC-ADDR DST-MAC-WILDCARD | host DST-MAC-ADDR | any} [{eq | lt
| gt | neq} PORT | range MIN-PORT MAX-PORT] [TCP-FLAG] [cos OUTER-COS] [vlan
OUTER-VLAN] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILENAME]
[SEQUENCE-NUMBER] {permit | deny} udp {SRC-IP-ADDR SRC-IP-WILDCARD | host SRCIP-ADDR | any} {SRC-MAC-ADDR SRC-MAC-WILDCARD | host SRC-MAC-ADDR | any} [{eq |
lt | gt | neq} PORT | range MIN-PORT MAX-PORT] {DST-IP-ADDR DST-IP-WILDCARD | host
DST-IP-ADDR | any} {DST-MAC-ADDR DST-MAC-WILDCARD | host DST-MAC-ADDR | any}
[{eq | lt | gt | neq} PORT | range MIN-PORT MAX-PORT] [cos OUTER-COS] [vlan OUTERVLAN] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} icmp {SRC-IP-ADDR SRC-IP-WILDCARD | host SRCIP-ADDR | any} {SRC-MAC-ADDR SRC-MAC-WILDCARD | host SRC-MAC-ADDR | any} {DST-
IP-ADDR DST-IP-WILDCARD | host DST-IP-ADDR | any} {DST-MAC-ADDR DST-MACWILDCARD | host DST-MAC-ADDR | any} [ICMP-TYPE [ICMP-CODE] | ICMP-MESSAGE] [cos
OUTER-COS] [vlan OUTER-VLAN] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP]
[time-range PROFILE-NAME]
no SEQUENCE-NUMBER
Parameters
SEQUENCE-NUMBER
Specifies the sequence number. The range is from 1 to 65535. The
lower the number is, the higher the priority of the permit/deny rule.
cos OUTER-COS
(Optional) Specifies the outer priority value. This value must be
between 0 and 7.
vlan OUTER-VLAN
(Optional) Specifies the outer VLAN ID.
any
Specifies to use any source MAC address, any destination MAC
address, any source IP address, or any destination IP address.
host SRC-MAC-ADDR
Specifies a specific source host MAC address.
SRC-MAC-ADDR SRC-MACWILDCARD
Specifies a group of source MAC addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to bit value 0 will be checked.
host DST-MAC-ADDR
Specifies a specific destination host MAC address.
DST-MAC-ADDR DST-MACWILDCARD
Specifies a group of destination MAC addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
PROTOCOL
(Optional) Specifies the IP protocol ID. Enter the following
keywords: eigrp, esp, gre, igmp, ospf, pim, vrrp, pcp, and ipinip.
host SRC-IP-ADDR
Specifies a specific source host IP address.
SRC-IP-ADDR SRC-IP-
Specifies a group of source IP addresses by using a wildcard
Page 55
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
52
WILDCARD
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
host DST-IP-ADDR
Specifies a specific destination host IP address.
DST-IP-ADDR DST-IPWILDCARD
Specifies a group of destination IP addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
precedence PRECEDENCE
(Optional) Specifies that packets can be filtered by precedence
level, as specified by a number from 0 to 7.
tos TOS
(Optional) Specifies that packets can be filtered by type of service
level, as specified by a number from 0 to 15.
dscp DSCP
(Optional) Specifies the matching DSCP code in IP header. The
range is from 0 to 63, or select the following DSCP name: af11 001010, af12 -001100, af13 - 001110, af21 - 010010, af22 010100, af23 - 010110, af31 - 011010, af32 - 011100, af33 011110, af41 - 100010, af42 - 100100, af43 - 100110, cs1 001000, cs2 - 010000, cs3 - 011000, cs4 - 100000, cs5 - 101000,
cs6 - 110000, cs7 - 111000, default - 000000, ef – 101110.
lt PORT
(Optional) Specifies to match if less than the specified port number.
gt PORT
(Optional) Specifies to match if greater than the specified port
number.
eq PORT
(Optional) Specifies to match if equal to the specified port number.
neq PORT
(Optional) Specifies to match if not equal to the specified port
number.
range MIN-PORT MAX-PORT
(Optional) Specifies to match if fall within the range of ports.
TCP-FLAG
(Optional) Specifies the TCP flag fields and the specified TCP
header bits called ack (acknowledge), fin (finish), psh (push), rst
(reset), syn (synchronize), or urg (urgent).
fragments
(Optional) Specifies the packet fragment’s filtering.
time-range PROFILE-NAME
(Optional) Specifies the name of time period profile associated with
the access list delineating its activation period.
ICMP-TYPE
(Optional) Specifies the ICMP message type. The valid number for
the message type is from 0 to 255.
ICMP-CODE
(Optional) Specifies the ICMP message code. The valid number for
the message code is from 0 to 255.
ICMP-MESSAGE
(Optional) Specifies the ICMP message. The following pre-defined
parameters are available for selection: beyond-scope, destinationunreachable, echo-reply, echo-request, header, hop-limit, mldquery, mld-reduction, mld-report, nd-na, nd-ns, next-header, noadmin, no-route, packet-too-big, parameter-option, parameterproblem, port-unreachable, reassembly-timeout, redirect, renumcommand, renum-result, renum-seq-number, router-advertisement,
router-renumbering, router-solicitation, time-exceeded,
unreachable.
Default
None.
Command Mode
Extended Expert Access-list Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Page 56
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
53
If a rule entry is created without a sequence number, a sequence number will be automatically
assigned. If it is the first entry, the sequence number 10 is assigned. A subsequent rule entry will be
assigned a sequence number that is 10 greater than the largest sequence number in that access list
and is placed at the end of the list.
The user can use the command access-list sequence to change the start sequence number and
increment number for the specified access list. After the command is applied, the new rule without
specified sequence number will be assigned sequence based new sequence setting of the specified
access list.
When you manually assign the sequence number, it is better to have a reserved interval for future
lower sequence number entries. Otherwise, it will create extra effort to insert an entry with a lower
sequence number.
The sequence number must be unique in the domain of an access-list. If you enter a sequence
number that is already present, an error message will be shown.
Example
This example shows how to use the extended expert ACL. The purpose is to deny all the TCP
packets with the source IP address 192.168.4.12 and the source MAC address 00:13:00:49:82:72.
Switch# configure terminal
Switch(config)# expert access-list extended exp_acl
Switch(config-exp-nacl)# deny tcp host 192.168.4.12 host 0013.0049.8272 any any
Switch(config-exp-nacl)# end
Switch# show access-lists
Extended Expert access list exp_acl(ID: 9999)
10 deny tcp host 192.168.4.12 host 0013.0049.8272 any any
Switch#
4-18 permit | deny (ip access-list)
This command is used to add a permit or a deny entry. Use the no form of this command to remove
an entry.
Extended Access List:
[SEQUENCE-NUMBER] {permit | deny} tcp {any | host SRC-IP-ADDR | SRC-IP-ADDR SRC-IP-
WILDCARD} [{eq | lt | gt | neq} PORT | range MIN-PORT MAX-PORT] {any | host DST-IP-
ADDR | DST-IP-ADDR DST-IP-WILDCARD} [{eq | lt | gt | neq} PORT | range MIN-PORT MAXPORT] [TCP-FLAG] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range
PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} udp {any | host SRC-IP-ADDR | SRC-IP-ADDR SRCIP-WILDCARD} [{eq | lt | gt | neq} PORT | range MIN-PORT MAX-PORT] {any | host DST-IP-
ADDR | DST-IP-ADDR DST-IP-WILDCARD} [{eq | lt | gt | neq} PORT | range MIN-PORT MAXPORT] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} icmp {any | host SRC-IP-ADDR | SRC-IP-ADDR SRCIP-WILDCARD} {any | host DST-IP-ADDR | DST-IP-ADDR DST-IP-WILDCARD} [ICMP-TYPE
[ICMP-CODE] | ICMP-MESSAGE] [[precedence PRECEDENCE] [tos TOS] | dscp DSCP]
[time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} {gre | esp | eigrp | igmp | ipinip | ospf | pcp | pim |
vrrp | protocol-id PROTOCOL-ID} {any | host SRC-IP-ADDR | SRC-IP-ADDR SRC-IP-
WILDCARD} {any | host DST-IP-ADDR | DST-IP-ADDR DST-IP-WILDCARD} [fragments]
[[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} {any | host SRC-IP-ADDR | SRC-IP-ADDR SRC-IP-
WILDCARD} [any | host DST-IP-ADDR | DST-IP-ADDR DST-IP-WILDCARD] [fragments]
[[precedence PRECEDENCE] [tos TOS] | dscp DSCP] [time-range PROFILE-NAME]
Page 57
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
54
Standard IP Access List:
[SEQUENCE-NUMBER] {permit | deny} {any | host SRC-IP-ADDR | SRC-IP-ADDR SRC-IP-
WILDCARD} [any | host DST-IP-ADDR | DST-IP-ADDR DST-IP-WILDCARD] [time-range
PROFILE-NAME]
no SEQUENCE-NUMBER
Parameters
SEQUENCE-NUMBER
Specifies the sequence number. The range is from 1 to 65535. The
lower the number is, the higher the priority of the permit/deny rule.
any
Specifies any source IP address or any destination IP address.
host SRC-IP-ADDR
Specifies a specific source host IP address.
SRC-IP-ADDR SRC-IPWILDCARD
Specifies a group of source IP addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
host DST-IP-ADDR
Specifies a specific destination host IP address.
DST-IP-ADDR DST-IPWILDCARD
Specifies a group of destination IP addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
precedence PRECEDENCE
(Optional) Specifies that packets can be filtered by precedence
level, as specified by a number from 0 to 7.
dscp DSCP
(Optional) Specifies the matching DSCP code in IP header. The
range is from 0 to 63, or select the following DSCP name: af11 001010, af12 -001100, af13 - 001110, af21 - 010010, af22 010100, af23 - 010110, af31 - 011010, af32 - 011100, af33 011110, af41 - 100010, af42 - 100100, af43 - 100110, cs1 - 001000,
cs2 - 010000, cs3 - 011000, cs4 - 100000, cs5 - 101000, cs6 110000, cs7 - 111000, default - 000000, ef – 101110.
tos TOS
(Optional) Specifies that packets can be filtered by type of service
level, as specified by a number from 0 to 15.
lt PORT
(Optional) Specifies to match if less than the specified port number.
gt PORT
(Optional) Specifies to match if greater than the specified port
number.
eq PORT
(Optional) Specifies to match if equal to the specified port number.
neq PORT
(Optional) Specifies to match if not equal to the specified port
number.
range MIN-PORT MAX-PORT
(Optional) Specifies to match if fall within the range of ports.
TCP-FLAG
(Optional) Specifies the TCP flag fields and the specified TCP
header bits called ack (acknowledge), fin (finish), psh (push), rst
(reset), syn (synchronize), or urg (urgent).
fragments
(Optional) Specifies the packet fragment’s filtering.
time-range PROFILE-NAME
(Optional) Specifies the name of the time period profile associated
with the access list delineating its activation period.
tcp, udp, igmp, ipinip, gre,
esp, eigrp, ospf, pcp, pim,
vrrp
Specifies Layer 4 protocols.
PROTOCOL-ID
(Optional) Specifies the protocol ID. The valid value is from 0 to
255.
ICMP-TYPE
(Optional) Specifies the ICMP message type. The valid number for
the message type is from 0 to 255.
ICMP-CODE
(Optional) Specifies the ICMP message code. The valid number for
Page 58
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
55
the message code is from 0 to 255.
ICMP-MESSAGE
(Optional) Specifies the ICMP message. The pre-defined
parameters are available for selection: administrativelyprohibited,alternate-address,conversion-error,host-prohibited,netprohibited,echo,echo-reply,pointer-indicates-error,hostisolated,host-precedence-violation,host-redirect,host-tosredirect,host-tos-unreachable,host-unknown,host-unreachable,
information-reply,information-request,mask-reply,maskrequest,mobile-redirect,net-redirect,net-tos-redirect,net-tosunreachable, net-unreachable,net-unknown,bad-length,optionmissing,packet-fragment,parameter-problem,portunreachable,precedence-cutoff, protocol-unreachable,reassemblytimeout,redirect-message,router-advertisement,routersolicitation,source-quench,source-route-failed, timeexceeded,timestamp-reply,timestamp-request,traceroute,ttlexpired,unreachable.
Default
None.
Command Mode
IP Access-list Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
If a rule entry is created without a sequence number, a sequence number will be automatically
assigned. If it is the first entry, the sequence number 10 is assigned. A subsequent rule entry will be
assigned a sequence number that is 10 greater than the largest sequence number in that access list
and is placed at the end of the list.
The user can use the command access-list sequence to change the start sequence number and
increment number for the specified access list. After the command is applied, the new rule without
specified sequence number will be assigned sequence based new sequence setting of the specified
access list.
When you manually assign the sequence number, it is better to have a reserved interval for future
lower sequence number entries. Otherwise, it will create extra effort to insert an entry with a lower
sequence number.
The sequence number must be unique in the domain of an access-list. If you enter a sequence
number that is already present, an error message will be shown.
To create a matching rule for an IP standard access list, only the source IP address or destination IP
address fields can be specified.
Example
This example shows how to create four entries for an IP extended access list, named Strict-Control.
These entries are: permit TCP packets destined to network 10.20.0.0, permit TCP packets destined to
host 10.100.1.2, permit all TCP packets go to TCP destination port 80 and permit all ICMP packets.
Switch# configure terminal
Switch(config)# ip extended access-list Strict-Control
Switch(config-ip-ext-acl)# permit tcp any 10.20.0.0 0.0.255.255
Switch(config-ip-ext-acl)# permit tcp any host 10.100.1.2
Switch(config-ip-ext-acl)# permit tcp any any eq 80
Switch(config-ip-ext-acl)# permit icmp any any
Switch(config-ip-ext-acl)#
This example shows how to create two entries for an IP standard access-list, named “std-ip”. These
entries are: permit IP packets destined to network 10.20.0.0, permit IP packets destined to host
10.100.1.2.
Page 59
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
56
Switch# configure terminal
Switch(config)# ip access-list std-acl
Switch(config-ip-acl)# permit any 10.20.0.0 0.0.255.255
Switch(config-ip- acl)# permit any host 10.100.1.2
Switch(config-ip- acl)#
4-19 permit | deny (ipv6 access-list)
This command is used to add a permit entry or deny entry to the IPv6 access list. Use the no form of
this command to remove an entry from the IPv6 access list.
Extended IPv6 Access List:
[SEQUENCE-NUMBER] {permit | deny} tcp {any | host SRC-IPV6-ADDR | SRC-IPV6-
ADDR/PREFIX-LENGTH} [{eq | lt | gt | neq} PORT | range MIN-PORT MAX-PORT] {any | host
DST-IPV6-ADDR | DST-IPV6-ADDR/PREFIX-LENGTH} [{eq | lt | gt | neq} PORT | range MIN-
PORT MAX-PORT] [TCP-FLAG] [dscp VALUE] [flow-label FLOW-LABEL] [time-range
PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} udp {any | host SRC-IPV6-ADDR | SRC-IPV6ADDR/PREFIX-LENGTH} [{eq | lt | gt | neq} PORT | range MIN-PORT MAX-PORT] {any | host
DST-IPV6-ADDR | DST-IPV6-ADDR/PREFIX-LENGTH} [{eq | lt | gt | neq} PORT | range MINPORT MAX-PORT] [dscp VALUE] [flow-label FLOW-LABEL] [time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} icmp {any | host SRC-IPV6-ADDR | SRC-IPV6ADDR/PREFIX-LENGTH} {any | host DST-IPV6-ADDR | DST-IPV6-ADDR/PREFIX-LENGTH}
[ICMP-TYPE [ICMP-CODE] | ICMP-MESSAGE] [dscp VALUE] [flow-label FLOW-LABEL] [timerange PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} {esp | pcp | sctp | protocol-id PROTOCOL-ID} {any |
host SRC-IPV6-ADDR | SRC-IPV6-ADDR/PREFIX-LENGTH} {any | host DST-IPV6-ADDR |
DST-IPV6-ADDR/PREFIX-LENGTH} [fragments] [dscp VALUE] [flow-label FLOW-LABEL]
[time-range PROFILE-NAME]
[SEQUENCE-NUMBER] {permit | deny} {any | host SRC-IPV6-ADDR | SRC-IPV6-
ADDR/PREFIX-LENGTH} [any | host DST-IPV6-ADDR | DST-IPV6-ADDR/PREFIX-LENGTH]
[fragments] [dscp VALUE] [flow-label FLOW-LABEL] [time-range PROFILE-NAME]
Standard IPv6 Access List:
[SEQUENCE-NUMBER] {permit | deny} {any | host SRC-IPV6-ADDR | SRC-IPV6-
ADDR/PREFIX-LENGTH} [any | host DST-IPV6-ADDR | DST-IPV6-ADDR/PREFIX-LENGTH]
[time-range PROFILE-NAME]
no SEQUENCE-NUMBER
Parameters
SEQUENCE-NUMBER
Specifies the sequence number. The range is from 1 to 65535. The
lower the number is, the higher the priority of the permit/deny rule.
any
Specifies any source IPv6 address or any destination IPv6 address.
host SRC-IPV6-ADDR
Specifies a specific source host IPv6 address.
SRC-IPV6-ADDR/PREFIXLENGTH
Specifies a source IPv6 network.
host DST-IPV6-ADDR
Specifies a specific destination host IPv6 address.
DST-IPV6-ADDR/PREFIXLENGTH
Specifies a destination IPv6 network.
tcp, udp, icmp, esp,
Specifies the Layer 4 protocol type.
Page 60
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
57
pcp ,sctp
dscp VALUE
(Optional) Specifies the matching traffic class value in IPv6 header.
The range is from 0 to 63, or select the following DSCP name: af11
- 001010, af12 -001100, af13 - 001110, af21 - 010010, af22 010100, af23 - 010110, af31 - 011010, af32 - 011100, af33 011110, af41 - 100010, af42 - 100100, af43 - 100110, cs1 - 001000,
cs2 - 010000, cs3 - 011000, cs4 - 100000, cs5 - 101000, cs6 110000, cs7 - 111000, default - 000000, ef – 101110.
lt PORT
(Optional) Specifies to match if less than the specified port number.
gt PORT
(Optional) Specifies to match if greater than the specified port
number.
eq PORT
(Optional) Specifies to match if equal to the specified port number.
neq PORT
(Optional) Specifies to match if not equal to the specified port
number.
range MIN-PORT MAX-PORT
(Optional) Specifies to match if fall within the range of ports.
PROTOCOL-ID
(Optional) Specifies the protocol ID. The valid value is from 0 to
255.
ICMP-TYPE
(Optional) Specifies the ICMP message type. The valid number of
the message type is from 0 to 255.
ICMP-CODE
(Optional)Specifies the ICMP message code. The valid number of
the code type is from 0 to 255.
ICMP-MESSAGE
(Optional) Specifies the ICMP message. The following pre-defined
parameters are available for selection: beyond-scope, destinationunreachable, echo-reply, echo-request, erroneous_header, hoplimit, multicast-listener-query, multicast-listener-done, multicastlistener-report, nd-na, nd-ns, next-header, no-admin, no-route,
packet-too-big, parameter-option, parameter-problem, portunreachable, reassembly-timeout, redirect, renum-command,
renum-result, renum-seq-number, router-advertisement, routerrenumbering, router-solicitation, time-exceeded, unreachable.
TCP-FLAG
(Optional) Specifies the TCP flag fields and the specified TCP
header bits called ack (acknowledge), fin (finish), psh (push), rst
(reset), syn (synchronize), or urg (urgent).
flow-label FLOW-LABEL
(Optional) Specifies the flow label value, within the range of 0 to
1048575.
fragments
(Optional) Specifies the packet fragment’s filtering.
time-range PROFILE-NAME
(Optional) Specifies the name of time period profile associated with
the access list delineating its activation period.
Default
None.
Command Mode
IPv6 Access-list Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
If a rule entry is created without a sequence number, a sequence number will be automatically
assigned. If it is the first entry, the sequence number 10 is assigned. A subsequent rule entry will be
assigned a sequence number that is 10 greater than the largest sequence number in that access list
and is placed at the end of the list.
The user can use the command access-list sequence to change the start sequence number and
increment number for the specified access list. After the command is applied, the new rule without
Page 61
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
58
specified sequence number will be assigned sequence based new sequence setting of the specified
access list.
When you manually assign the sequence number, it is better to have a reserved interval for future
lower sequence number entries. Otherwise, it will create extra effort to insert an entry with a lower
sequence number.
The sequence number must be unique in the domain of an access-list. If you enter a sequence
number that is already present, an error message will be shown.
Example
This example shows how to create four entries for an IPv6 extended access list named “ipv6-control”.
These entries are: permit TCP packets destined to network ff02::0:2/16, permit TCP packets destined
to host ff02::1:2, permit all TCP packets go to port 80 and permit all ICMP packets.
Switch# configure terminal
Switch(config)# ipv6 access-list extended ipv6-control
Switch(config-ipv6-ext-acl)# permit tcp any ff02::0:2/16
Switch(config-ipv6-ext-acl)# permit tcp any host ff02::1:2
Switch(config-ipv6-ext-acl)# permit tcp any any eq 80
Switch(config-ipv6-ext-acl)# permit icmp any any
Switch(config-ipv6-ext-acl)#
This example shows how to create two entries for an IPv6 standard access-list named “ipv6-std-
control”. These entries are: permit IP packets destined to network ff02::0:2/16, and permit IP packets
destined to host ff02::1:2.
Switch# configure terminal
Switch(config)# ipv6 access-list ipv6-std-control
Switch(config-ipv6-acl)# permit any ff02::0:2/16
Switch(config-ipv6-acl)# permit any host ff02::1:2
Switch(config-ipv6-acl)#
4-20 permit | deny (mac access-list)
This command is used to define the rule for packets that will be permitted or denied. Use the no form
of this command to remove an entry
[SEQUENCE-NUMBER] {permit | deny} {any | host SRC-MAC-ADDR | SRC-MAC-ADDR SRCMAC-WILDCARD} {any | host DST-MAC-ADDR | DST-MAC-ADDR DST-MAC-WILDCARD}
[ethernet-type TYPE MASK [cos VALUE] [vlan VLAN-ID] [time-range PROFILE-NAME]
no SEQUENCE-NUMBER
Parameters
SEQUENCE-NUMBER
Specifies the sequence number. The range is from 1 to 65535. The
lower the number is, the higher the priority of the permit/deny rule.
any
Specifies any source MAC address or any destination MAC
address.
host SRC-MAC-ADDR
Specifies a specific source host MAC address.
SRC-MAC-ADDR SRC-MACWILDCARD
Specifies a group of source MAC addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
bit corresponding to the bit value 0 will be checked.
host DST-MAC-ADDR
Specifies a specific destination host MAC address.
DST-MAC-ADDR DST-MACWILDCARD
Specifies a group of destination MAC addresses by using a wildcard
bitmap. The bit corresponding to the bit value 1 will be ignored. The
Page 62
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
59
bit corresponding to the bit value 0 will be checked.
ethernet-type TYPE MASK
(Optional) Specifies that the Ethernet type which is a hexadecimal
number from 0 to FFFF or the name of an Ethernet type which can
be one of the following: aarp, appletalk, decnet-iv, etype-6000,
etype-8042, lat, lavc-sca, mop-console, mop-dump, vines-echo,
vines-ip, xns-idp., arp.
cos VALUE
(Optional) Specifies the priority value of 0 to 7.
vlan VLAN-ID
(Optional) Specifies the VLAN-ID.
time-range PROFILE-NAME
(Optional) Specifies the name of time period profile associated with
the access list delineating its activation period
Default
None.
Command Mode
MAC Access-list Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
If a rule entry is created without a sequence number, a sequence number will be automatically
assigned. If it is the first entry, the sequence number 10 is assigned. A subsequent rule entry will be
assigned a sequence number that is 10 greater than the largest sequence number in that access list
and is placed at the end of the list.
The user can use the command access-list sequence to change the start sequence number and
increment number for the specified access list. After the command is applied, the new rule without
specified sequence number will be assigned sequence based new sequence setting of the specified
access list.
When you manually assign the sequence number, it is better to have a reserved interval for future
lower sequence number entries. Otherwise, it will create extra effort to insert an entry with a lower
sequence number.
The sequence number must be unique in the domain of an access-list. If you enter a sequence
number that is already present, an error message will be displayed.
Multiple entries can be added to the list, and you can use permit for one entry and use deny for the
other entry. Different permit and deny commands can match different fields available for setting.
Example
This example shows how to configure MAC access entries in the profile daily-profile to allow two sets
of source MAC addresses.
Switch# configure terminal
Switch(config)# mac access-list extended daily-profile
Switch(config-mac-ext-acl)# permit 00:80:33:00:00:00 00:00:00:ff:ff:ff any
Switch(config-mac-ext-acl)# permit 00:f4:57:00:00:00 00:00:00:ff:ff:ff any
Switch(config-mac-ext-acl)#
4-21 show access-group
This command is used to display access group information for interface(s).
show access-group [interface INTERFACE-ID]
Parameters
Page 63
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
60
interface INTERFACE-ID
(Optional) Specifies the interface to be displayed.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
If interface is not specified, all of the interfaces that have access list configured will be displayed.
Example
This example shows how to display access lists that are applied to all of the interfaces.
Switch# show access-group
eth1/0/1:
Inbound mac access-list : simple-mac-acl(ID: 7998)
Inbound ip access-list : simple-ip-acl(ID: 1998)
Switch#
4-22 show access-list
This command is used to display the access list configuration information.
show access-list [ip [NAME | NUMBER] | mac [NAME | NUMBER] | ipv6 [NAME | NUMBER] |
expert [NAME | NUMBER] | arp [NAME]]
Parameters
ip
(Optional) Specifies to display a listing of all IP access lists.
mac
(Optional) Specifies to display a listing of all MAC access lists.
ipv6
(Optional) Specifies to display a listing of all IPv6 access lists.
expert
(Optional) Specifies to display a listing of all expert access lists.
NAME | NUMBER
Specifies to display the contents of the specified access list.
arp
Specifies to display the ARP access list.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
This command displays access list information. If no option is specified, a listing of all configured
access lists is displayed. If the type of access list is specified, detailed information of the access list
Page 64
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
61
will be displayed. If the user enables the ACL hardware counter for an access list, the counter will be
displayed based on each access list entry.
Example
This example shows how to display all access lists.
Switch# show access-list
Access-List-Name Type
-------------------------------------- ---------------
simple-ip-acl(ID: 3998) ip ext-acl
simple-rd-acl(ID: 3999) ip ext-acl
rd-mac-acl(ID: 6998) mac ext-acl
rd-ip-acl(ID: 1998) ip acl
ip6-acl(ID: 12999) ipv6 ext-acl
park-arp-acl arp acl
Total Entries: 6
Switch#
This example shows how to display the IP access list called R&D.
Switch# show access-list ip R&D
IP access list R&D(ID:3996)
10 permit tcp any 10.20.0.0 0.0.255.255
20 permit tcp any host 10.100.1.2
30 permit icmp any any
Switch#
This example shows how to display the content for the access list if its hardware counter is enabled.
Switch# show access-list ip simple-ip-acl
IP access list simple-ip-acl(ID:3994)
10 permit tcp any 10.20.0.0 0.0.255.255 (Ing: 12410 packets)
20 permit tcp any host 10.100.1.2 (Ing: 6532 packets)
30 permit icmp any any (Ing: 8758 packets)
Counter enable on following port(s):
Ingress port(s): eth1/0/5-eth1/0/8
Switch#
4-23 show vlan access-map
This command is used to display the VLAN access-map configuration information.
show vlan access-map [MAP-NAME]
Parameters
MAP-NAME
(Optional) Specifies the name of the VLAN access map being
Page 65
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
62
configured. The name can be up to 32 characters.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
If no access-map name is specified, all VLAN access-map information will be displayed. If the user
enables the ACL hardware counter for an access-map, the counter will be displayed based on each
sub-map.
Example
This example shows how to display the VLAN access-map.
Switch# show vlan access-map
VLAN access-map vlan-map 10
match ip access list: stp_ip1(ID: 1888)
action: forward
VLAN access-map vlan-map 20
match mac access list: ext_mac(ID: 6995)
action: redirect eth1/0/5
Switch#
This example shows how to display the contents of the VLAN access-map if its hardware counter is
enabled.
Switch# show vlan access-map
VLAN access-map vlan-map 10
match ip access list: stp_ip1(ID: 1888)
action: forward
Counter enable on VLAN(s): 1-2
match count: 8541 packets
VLAN access-map vlan-map 20
match mac access list: ext_mac(ID: 6995)
action: redirect eth1/0/5
Counter enable on VLAN(s): 1-2
match count: 5647 packets
Switch#
4-24 show vlan filter
This command is used to display the VLAN filter configuration of VLAN interfaces.
show vlan filter [access-map MAP-NAME | vlan VLAN-ID]
Parameters
Page 66
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
63
MAP-NAME
(Optional) Specifies the name of the VLAN access map. The name
can be up to 32 characters.
VLAN-ID
(Optional) Specifies the VLAN ID.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
The show vlan filter access-map command is used to display the VLAN filter information by access
map. The command show vlan filter vlan is used to display the VLAN filter information by VLAN.
Example
This example shows how to display VLAN filter information.
Switch# show vlan filter
VLAN Map aa
Configured on VLANs: 5-127,221-333
VLAN Map bb
Configured on VLANs: 1111-1222
Switch#
Switch# show vlan filter vlan 5
VLAN ID 5
VLAN Access Map: aa
Switch#
4-25 vlan access-map
This command is used to create a sub-map of a VLAN access map and enter the VLAN access-map
sub-map configure mode. The no form of this command used to delete an access-map or its sub-map.
vlan access-map MAP-NAME [SEQUENCE-NUM]
no vlan access-map MAP-NAME [SEQUENCE-NUM]
Parameters
MAP-NAME
Specifies the name of the VLAN access map to be configured. The
name can be up to 32 characters.
SEQUENCE-NUM
(Optional) Specifies the sequence number of the sub-map. The
valid range is from 1 to 65535.
Default
None.
Command Mode
Page 67
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
64
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
A VLAN access map can contain multiple sub-maps. For each sub-map, one access list (IP access
list, IPv6 access list or MAC access list) can be specified and one action can be specified. After a
VLAN access map is created, the user can use the vlan filter command to apply the access map to
VLAN(s).
A sequence number will be assigned automatically if the user does not assign it manually, and the
automatically assigned sequence number starts from 10, and increase 10 per new entry.
The packet that matches the sub-map (that is packet permitted by the associated access-list) will take
the action specified for the sub-map. No further check against the next sub-maps is done. If the
packet does not match a sub-map, then the next sub-map will be checked.
Using the no form of this command without specify sequence numbers, will delete all sub-map
information of the specified access-map.
Example
This example shows how to create a VLAN access map.
Switch# configure terminal
Switch(config)# vlan access-map vlan-map 20
Switch(config-access-map)#
4-26 vlan filter
This command is used to apply a VLAN access map in a VLAN. Use the no form of this command to
remove a VLAN access map from the VLAN.
vlan filter MAP-NAME vlan-list VLAN-ID-LIST
no vlan filter MAP-NAME vlan-list VLAN-ID-LIST
Parameters
MAP-NAME
Specifies the name of the VLAN access map.
VLAN-ID-LIST
Specifies the VLAN ID list.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
A VLAN can only be associated with one VLAN access map.
Example
This example shows how to apply the VLAN access-map “vlan-map” in VLAN 5.
Page 68
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
65
Switch# configure terminal
Switch(config)# vlan filter vlan-map vlan-list 5
Switch(config-access-map)# end
Switch# show vlan filter
VLAN Map vlan-map
Configured on VLANs: 5
Switch#
Page 69
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
66
5. Access Management Commands
5-1 access class
This command is used to specify an access list to restrict the access via a line. Use the no form of
this command to remove the specified access list check.
access-class IP-ACL
no access-class IP-ACL
Parameters
IP-ACL
Specifies a standard IP access list. The source address field of the
permit or deny entry define the valid or invalid host.
Default
None.
Command Mode
Line Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
This command specifies access lists to restrict the access via a line. At most two access lists can be
applied to a line. If two access lists are already applied, an attempt to apply a new access list will be
rejected until an applied access list is removed by the no form of this command.
Example
This example shows how a standard IP access list is created and is specified as the access list to
restrict access via Telnet. Only the host 226.1.1.1 is allowed to access the server.
Switch# configure terminal
Switch(config)# ip access-list vty-filter
Switch(config-ip-acl)# permit 226.1.1.1 0.0.0.0
Switch(config-ip-acl)# exit
Switch(config)# line telnet
Switch(config-line)# access-class vty-filter
Switch(config-line)#
5-2 prompt
This command is used to customize the CLI prompt. Use the no form of this command to revert to the
default setting.
prompt STRING
no prompt
Parameters
STRING
Specifies a string to customize the CLI prompt. The prompt will be composed
based on the specified characters or the following control characters. The
Page 70
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
67
space character in the string is ignored.
% h - Specifies to encode the SNMP server name.
%s - Specifies to have space.
%% - Specifies to encode the % symbol.
Default
By default, the string is the same as the SNMP server name.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to customize the CLI prompt.
If the user selects to encode the SNMP server name as the prompt, only the first 15 characters are
encoded.
The privileged level character will appear as the last character of the prompt. The character is defined
as follows.
> - Represents user level.
# - Represents privileged user level.
Example
This example shows how to change the prompt to “BRANCH A”.
Switch#configure terminal
Switch(config)#prompt BRANCH%sA
BRANCH A(config)#
This example shows how to set the command prompt back to the default setting.
BRANCH A#configure terminal
BRANCH A(config)#no prompt
Switch(config)#
5-3 enable password
This command is used to setup enable password to enter different privileged levels. Use the no form
of this command to return the password to the empty string.
enable password [level PRIVILEGE-LEVEL] [0| 7 | 15] PASSWORD
no enable password [level PRIVILEGE-LEVEL]
Parameters
level PRIVILEGE-LEVEL
Specifies the privilege level for the user. The privilege level is
between 1 and 15. If this argument is not specified in the command
or the no form of the command, the privilege level defaults to 15
(traditional enable privileges).
0 PASSWORD
Specifies the password the user must enter to gain access to the
Switch. The password can contain embedded spaces. The
password is case-sensitive. This is the default option. The plain-text
password maximum length is 32. (The range is 1-32)
Page 71
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
68
7 PASSWORD
Specifies the password in the encrypted form based on SHA-1. For
the encrypted form password, the length is fixed to 35 bytes long.
The password is case-sensitive. The syntax is Encrypted Password.
15 PASSWORD
Specifies the password in the encrypted form based on MD5. For
the encrypted form password, the length is fixed to 31 bytes long.
The password is case-sensitive. The syntax is Encrypted Password.
Default
By default, no password is set. It is an empty string.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
The exact password for a specific level needs to be used to enter the privilege level. Each level has
only one password to enter the level.
Example
This example shows how to create an enable password at the privilege level 15 of
“MyEnablePassword”.
Switch# configure terminal
Switch(config) #enable password MyEnablePassword
Switch# disable
Switch# enable
Password:****************
Switch# show privilege
Current privilege level is 15
Switch#
5-4 ip http server
This command is used to enable the HTTP server. Use the no form of this command to disable the
HTTP server function.
ip http server
no ip http server
Parameters
None.
Default
By default, this option is enabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command enables the HTTP server function. The HTTPs access interface is separately
controlled by SSL commands.
Page 72
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
69
Example
This example shows how to enable the HTTP server.
Switch# configure terminal
Switch(config)# ip http server
Switch(config)#
5-5 ip http secure-server
This command is used to enable the HTTPS server. Use the ip http secure-server ssl-servicepolicy command to specify which SSL service policy is used for HTTPS. Use the no form of this
command to disable the HTTPS server function.
ip http secure-server [ssl-service-policy POLICY-NAME]
no ip http secure-server
Parameters
POLICY-NAME
(Optional) Specifies the SSL service policy name. Use this sslservice-policy keyword only if you have already declared an SSL
service policy using the ssl-service-policy command. When no
keyword is specified, a built-in local certificate will be used for
HTTPS.
Default
By default, this option is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command enables the HTTPS server function and uses the specified SSL service policy for
HTTPS.
Example
This example shows how to enable the HTTPS server function and use the service policy called “sp1”
for HTTPS.
Switch# configure terminal
Switch(config)# ip http secure-server ssl-service-policy sp1
Switch(config)#
5-6 ip http access-class
This command is used to specify an access list to restrict the access to the HTTP server. Use the no
form of this command to remove the access list check.
ip http access-class IP-ACL
no ip http access-class IP-ACL
Page 73
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
70
Parameters
IP-ACL
Specifies a standard IP access list. The source address field of the
entry defines the valid or invalid host.
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command specifies an access list to restrict the access to the HTTP server. If the specified
access list does not exist, the command does not take effect, thus no access list is checked for the
user’s access to HTTP.
Example
This example shows how a standard IP access list is created and is specified as the access list to
access the HTTP server. Only the host 226.1.1.1 is allowed to access the server.
Switch# configure terminal
Switch(config)# ip access-list http-filter
Switch(config-ip-acl)# permit 226.1.1.1 255.255.255.255
Switch(config-ip-acl)# exit
Switch(config)# ip http access-class http-filter
Switch(config)#
5-7 ip http service-port
This command is used to specify the HTTP service port. Use the no form of this command to return
the service port to 80.
ip http service-port TCP-PORT
no ip http service-port
Parameters
TCP-PORT
Specifies the TCP port number. TCP ports are numbered between 1
and 65535. The “well-known” TCP port for the HTTP protocol is 80.
Default
By default, this port number is 80.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command configures the TCP port number for the HTTP server.
Example
Page 74
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
71
This example shows how to configure the HTTP TCP port number to 8080.
Switch# configure terminal
Switch(config)# ip http service-port 8080
Switch(config)#
5-8 ip http timeout-policy idle
This command is used to set idle timeout of a http server connection in seconds. Use the no form of
this command to set the idle timeout to default value.
ip http timeout-policy idle INT
no ip http timeout-policy idle
Parameters
INT
Specifies the idle timeout value. This value is between 60 and
36000.
Default
By default, this value is 180 seconds.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is use to configure the idle timeout value of a http server connection in seconds.
Example
This example shows how to configure the idle timeout value to 100 seconds .
Switch#configure terminal
Switch(config)#ip http timeout-policy idle 100
Switch(config)#
5-9 ip telnet server
This command is used to enable a Telnet server. Use the no form of this command to disable the
Telnet server function
ip telnet server
no ip telnet server
Parameters
None.
Default
By default, this option is enabled.
Command Mode
Page 75
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
72
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command enables or disables the Telnet server. The SSH access interface is separately
controlled by SSH commands.
Example
This example shows how to enable the Telnet server.
Switch# configure terminal
Switch(config)# ip telnet server
Switch(config)#
5-10 ip telnet service-port
This command is used to specify the service port for Telnet. Use the no form of this command to
revert to the default setting.
ip telnet service-port TCP-PORT
no ip telnet service-port
Parameters
TCP-PORT
Specifies the TCP port number. TCP ports are numbered between 1
and 65535. The “well-known” TCP port for the TELNET protocol is
23.
Default
By default, this value is 23.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command configures the TCP port number for Telnet access
Example
This example shows how to change the Telnet service port number to 3000.
Switch# configure terminal
Switch(config)# ip telnet service-port 3000
Switch(config)#
5-11 line
This command is used to identify a line type for configuration and enter line configuration mode.
line {console | telnet | ssh}
Page 76
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
73
Parameters
console
Specifies the local console terminal line.
telnet
Specifies the Telnet terminal line
ssh
Specifies the SSH terminal line
Default
None.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
The line command is used to enter the Line Configuration Mode.
Example
This example shows how to enter the Line Configuration Mode for the SSH terminal line and
configures its access class as ”vty-filter”.
Switch# configure terminal
Switch(config)# line ssh
Switch(config-line)# access-class vty-filter
Switch(config-line)#
5-12 service password-encryption
This command is used to enable the encryption of the password before stored in the configuration file.
Use the no form of this command to disable the encryption.
service password-encryption [7 | 15]
no service password-encryption
Parameters
7
Specifies the password in the encrypted form based on SHA-1.
15
Specifies the password in the encrypted form based on MD5.
Default
By default, this option is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level:15.
Usage Guideline
The user account configuration information is stored in the running configuration file and can be
applied to the system later. If the service password-encryption command is enabled, the password
will be stored in the encrypted form.
Page 77
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
74
When the service password encryption option is disabled and the password is specified in the plain
text form, the password will be in plain text form. However, if the password is specified in the
encrypted form or if the password has been converted to the encrypted form by the last enable
password encryption option, the password will still be in the encrypted form. It cannot be reverted
back to plain text.
The password affected by this command includes the user account password, enable password, and
the authentication password.
Example
This example shows how to enable the encryption of the password before stored in the configuration
file.
Switch# configure terminal
Switch(config)# service password encryption
Switch(config)#
5-13 show terminal
This command is used to obtain information about the terminal configuration parameter settings for
the current terminal line. Use this command in any EXEC mode or any configuration mode.
show terminal
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to display information about the terminal configuration parameters for the current
terminal line.
Example
This example shows how to display information about the terminal configuration parameter settings
for the current terminal line.
Switch# show terminal
Terminal Settings:
Length: 24 lines
Width: 80 columns
Default Length: 24 lines
Default Width: 80 columns
Baud rate: 9600 bps
Switch#
Page 78
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
75
5-14 show ip telnet server
This command is used to obtain information about the Telnet server status. Use this command in any
EXEC mode or any configuration mode.
show ip telnet server
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to display information about the Telnet server status.
Example
This example shows how to display information about the Telnet server status.
Switch# show ip telnet server
Server State: Enabled
Switch#
5-15 show ip http server
This command is used to obtain information about the http server status. Use this command in EXEC
mode or any configuration mode.
show ip http server
Parameters
None.
Default
By default, the state is enabled.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to display information about the http server status.
Example
This example shows how to display information about the http server status.
Page 79
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
76
Switch#show ip http server
ip http server state : enable
Switch#
5-16 show ip http secure-server
This command is used to obtain information about the SSL status. Use this command in EXEC mode
or any configuration mode.
show ip http secure-server
Parameters
None.
Default
By default, the state is disabled.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to display information about the SSL status.
Example
This example shows how to display information about the SSL status.
Switch#show ip http secure-server
ip http secure-server state : disable
Switch#
5-17 show users
This command is used to display information about the active lines on the Switch.
show users
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Page 80
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
77
Usage Guideline
This command displays information about the active lines on the Switch.
Example
This example shows how to display all session information.
Switch# show users
ID Type User-Name Privilege Login-Time IP address
-------------------------------------------------------------------------------
0 * console admin 15 4S
Total Entries: 1
Switch#
5-18 telnet
This command is used to login another device that supports Telnet.
telnet [IP-ADDRESS | IPV6-ADDRESS | Domain Name] [TCP-PORT]
Parameters
IP-ADDRESS
Specifies the IPv4 address of the host.
IPV6-ADDRESS
Specifies the IPv6 address of the host.
Domain Name
Specifies the Telnet detination host name.
TCP-PORT
Specifies the TCP port number. TCP ports are numbered between 0
and 65535. The “well-known” TCP port for the Telnet protocol is 23
Default
None.
Command Mode
EXEC Mode.
Command Default Level
Level: 1.
Usage Guideline
This is the Telnet client function and can be used to communicate with another device using the
Telnet feature. The Telnet software supports special Telnet commands in the form of Telnet
sequences that map generic terminal control functions to operating system-specific functions. To
issue a special Telnet command, enter the escape sequence and then a command character. The
default escape sequence is CTRL+_ (press and hold the CTRL and Shift keys and the underscore ‘_’
key). The special Telnet commands will be displayed as follows:
e – Exits the Telnet connection. Either an uppercase or lowercase letter ‘e’ can exit the Telnet
connection.
If another key is pressed, the terminal will return to the original active Telnet session.
Multiple Telnet sessions can be opened on the Switch system and each open Telnet session can
have its own Telnet client software supported at the same time
Example
This example shows how to Telnet to the IP address 10.90.90.91 using the default port 23. The IP
address, 10.90.90.91 is the DGS-1510-28P management interface which allows a user to login.
Page 81
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
78
Switch# telnet 10.90.90.91
DGS-1510-28P Gigabit Ethernet SmartPro Switch
Command Line Interface
Firmware: Build 1.30.004
Copyright(C) 2015 D-Link Corporation. All rights reserved.
User Access Verification
Username:
This example shows how to Telnet through port 23 to 10.90.90.91 and the connection failed. Try
using port 3500 instead to login into the management interface.
Switch#telnet 10.90.90.91
ERROR: Could not open a connection to host on server port 23.
Switch# telnet 10.90.90.91 3500
DGS-1510-28P Gigabit Ethernet SmartPro Switch
Command Line Interface
Firmware: Build 1.30.004
Copyright(C) 2015 D-Link Corporation. All rights reserved.
User Access Verification
Username:
5-19 terminal length
The command is used to configure the number of lines displayed on the screen. The terminal length
command will only affect the current session. The terminal length default command will set the
default value but it doesn’t affect the current session. The newly created, saved session terminal
length will use the default value. Use the no form of this command to revert to the default setting.
terminal length NUMBER
no terminal length
terminal length default NUMBER
no terminal length default
Parameters
NUMBER
Specifies the number of lines to display on the screen. This value
must be between 0 and 512.When the terminal length is 0, the
display will not stop until it reaches the end of the display.
Default
By default, this value is 24.
Command Mode
Use the EXEC Mode or Privilege EXEC Mode for the terminal length command.
Use the Global Configuration Mode for the terminal length default command.
Page 82
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
79
Command Default Level
Level: 1 (for the terminal length command).
Level: 12 (for the terminal length default command).
Usage Guideline
When the terminal length is 0, the display will not stop until it reaches the end of the display.
If the terminal length is specified to a value other than 0, for example 50, then the display will stop
after every 50 lines. The terminal length is used to set the number of lines displayed on the current
terminal screen. This command also applies to Telnet and SSH sessions. Valid entries are from 0 to
512. The default is 24 lines. A selection of 0's instructs the Switch to scroll continuously (no pausing).
Output from a single command that overflows a single display screen is followed by the --More--
prompt. At the --More-- prompt, press CTRL+C, q, Q, or ESC to interrupt the output and return to the
prompt. Press the Spacebar to display an additional screen of output, or press Return to display one
more line of output. Setting the screen length to 0 turns off the scrolling feature and causes the entire
output to display at once. Unless the default keyword is used, a change to the terminal length value
applies only to the current session. When using the no form of this command, the number of lines in
the terminal display screen is reset to 24.
The terminal length default command is available in the global configuration mode. The command
setting does not affect the current existing terminal sessions but affects the new terminal sessions that
are activated later. Only the default terminal length value can be saved.
Example
This example shows how to change the lines to be displayed on a screen to 60.
Switch# terminal length 60
Switch#
5-20 terminal speed
This command is used to setup the terminal speed. Use the no form of this command to revert to the
default setting.
terminal speed BPS
no terminal speed
Parameters
BPS
Specifies the console rate in bits per second (bps).
Default
By default, this value is 115200.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to configure the terminal connection speed. Some baud rates available on the
devices connected to the port might not be supported on the Switch.
Example
This example shows how to configure the serial port baud rate to 9600 bps.
Page 83
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
80
Switch# configure terminal
Switch(config)# terminal speed 9600
Switch(config)#
5-21 session timeout
This command is used to configure the line session timeout value. Use the no form of this command
to revert to the default setting.
session-timeout MINUTES
no session-timeout
Parameters
MINUTES
Specifies the timeout length in minutes. 0 represents never timeout.
Default
By default, this value is 3 minutes.
Command Mode
Line Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This timer specifies the timeout for auto-logout sessions established by the line that is being
configured.
Example
This example shows how to configure the console session to never timeout.
Switch# configure terminal
Switch(config)# line console
Switch(config-line)# session-timeout 0
Switch(config-line)#
5-22 terminal width
The command is used to set the number of character columns on the terminal screen for the current
session line. The terminal width command will only affect the current session. The terminal width
default command will set the default value, but it doesn’t affect any current sessions.
terminal width NUMBER
no terminal width
terminal width default NUMBER
no terminal width default
Parameters
NUMBER
Specifies the number of characters to display on the screen. Valid
values are from 40 to 255.
Page 84
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
81
Default
By default, this value is 80 characters.
Command Mode
Use the EXEC Mode or Privilege EXEC Mode for the terminal width command.
Use the Global Configuration Mode for the terminal width default command.
Command Default Level
Level: 1 (for the terminal width command).
Level: 12 (for the terminal width default command).
Usage Guideline
By default, the Switch’s system terminal provides a screen display width of 80 characters. The
terminal width command changes the terminal width value which applies only to the current session.
When changing the value in a session, the value applies only to that session. When the no form of
this command is used, the number of lines in the terminal display screen is reset to the default, which
is 80 characters.
The terminal width default command is available in the global configuration mode. The command
setting does not affect the current existing terminal sessions but affect the new terminal sessions that
are activated later and just the global terminal width value can be saved.
However, for remote CLI session access such as Telnet, the auto-negotiation terminal width result will
take precedence over the default setting if the negotiation is successful. Otherwise, the default
settings take effect.
Example
This example shows how to adjust the current session terminal width to 120 characters.
Switch# show terminal
Length: 24 lines
Width: 80 columns
Default Length: 24 lines
Default Width: 80 columns
Baud rate: 9600
Switch# terminal width 120
Switch# show terminal
Length: 24 lines
Width: 120 columns
Default Length: 24 lines
Default Width: 80 columns
Baud rate: 9600
Switch #
5-23 username
This command is used to create a user account. Use the no form of this command to delete the user
account.
username NAME [privilege LEVEL] [nopassword | password [0 | 7 | 15] PASSWORD]
no username [NAME]
Parameters
Page 85
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
82
NAME
Specifies the user name with a maximum of 32 characters.
privilege LEVEL
(Optional) Specifies the privilege level for each user. The privilege
level must be between 1 and 15.
nopassword
(Optional) Specifies that there will be no password associated with
this account.
password
(Optional) Specifies the password for the user.
0
(Optional) Specifies the password in clear, plain text. The password
length is between 1 and 32 characters and can contain embedded
spaces. It is case-sensitive. If the password syntax cannot be
specified, the syntax remains plain text.
7
(Optional) Specifies the encrypted password based on SHA-1. The
password length is fixed at 35 bytes. It is case-sensitive. The
password is encrypted. If the password syntax is not specified, the
syntax is plain text.
15
(Optional) Specifies the encrypted password based on MD5. The
password length is fixed at 31 bytes. It is case-sensitive. The
password is encrypted. If the password syntax is not specified, the
syntax is plain text.
PASSWORD
(Optional) Specifies the password string based on the type.
Default
By default, the user name is admin, password is admin, and the privilege level is 15.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
This command creates user accounts with different access levels. When the user login with Level 1,
the user will be in the User EXEC Mode. The user needs to further use the enable command to enter
the Privileged EXEC Mode.
When the user login with a Level higher than or equal to 2, the user will directly enter the Privileged
EXEC Mode. Therefore, the Privileged EXEC Mode can be in Levels 2 to 15.
The user can specify the password in the encrypted form or in the plain-text form. If it is in the plaintext form, but the service password encryption option is enabled, the password will be converted to
the encrypted form.
If the no username command is used without the user name specified, all users are removed.
By default, the user account is empty. When the user account is empty, the user will be directly in the
User EXEC Mode at Level 1. The user can further enter the Privileged EXEC Mode using the enable
command.
Example
This example shows how to create an administrative username, called admin, and a password, called
“mypassword”.
Switch# configure terminal
Switch(config)# username admin privilege 15 password 0 mypassword
Switch(config)#
This example shows how to remove the user account with the username admin.
Page 86
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
83
Switch# configure terminal
Switch(config)# no username admin
Switch(config)#
5-24 password
This command is used to create a new password. Use the no form of this command remove the
password.
password [0 | 7 | 15] PASSWORD
no password
Parameters
0
Specifies the password in clear, plain text. The password length is
between 1 and 32 characters and can contain embedded spaces. It
is case-sensitive. If the password syntax cannot be specified, the
syntax remains plain text.
7
Specifies the encrypted password based on SHA-1. The password
length is fixed at 35 bytes. It is case-sensitive. The password is
encrypted. If the password syntax is not specified, the syntax is
plain text.
15
Specifies the encrypted password based on MD5. The password
length is fixed at 31 bytes. It is case-sensitive. The password is
encrypted. If the password syntax is not specified, the syntax is
plain text.
PASSWORD
Specifies the password for the user.
Default
None.
Command Mode
Line Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
This command is used to create a new user password. Only one password can be used for each type
of line.
Example
This example shows how to create a password for the console line.
Switch# configure terminal
Switch(config)# line console
Switch(config-line)# password 123
Switch(config-line)#
5-25 clear line
This command is used to disconnect an active session on the switch.
Page 87
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
84
clear line LINE-ID
Parameters
LINE-ID
Specifies the line ID to disconnect a connection session. The value
is from 1 to 22.
Default
None.
Command Mode
Privilege EXEC Mode.
Command Default Level
Level: 15.
Usage Guideline
This command is used to disconnect an active session on the switch.
Example
This example shows how to disconnect the line session 2.
Switch# clear line 1
Switch#
Page 88
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
85
6. ARP Spoofing Prevention Commands
6-1 ip arp spoofing-prevention
This command is used to configure an ARP Spoofing Prevention (ASP) entry of the gateway used for
preventing ARP poisoning attacks. Use the no form of this command to delete an ARP spoofing
prevention entry.
ip arp spoofing-prevention GATEWAY-IP GATEWAY-MAC interface INTERFACE-ID [,|-]
no ip arp spoofing-prevention GATEWAY-IP [interface INTERFACE-ID [,|-] ]
Parameters
GATEWAY-IP
Specifies the IP address of the gateway.
GATEWAY-MAC
Specifies the MAC address of the gateway. The MAC address
setting will replace the last configuration for the same gateway IP
address.
INTERFACE-ID
Specifies the interface that will be activated or removed from active
interface list (in the no form of this command). An ARP entry won't
be checked, if the receiving port is not included in the specified
interface list.
,
(Optional) Specifies a number of interfaces or separate a range of
interfaces from a previous range. No space before and after the
comma.
-
(Optional) Specifies a range of interfaces. No space before and
after the hyphen.
Default
By default, no entries exist.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
This command is used to configure the ARP spoofing prevention (ASP) entry to prevent spoofing of
the MAC address of the protected gateway. When an entry is created, ARP packets whose sender IP
address matches the gateway IP address, of an entry, but its sender MAC address field does not
match the gateway MAC address, of the entry, will be dropped by the system. The ASP will bypass
the ARP packets whose sender IP address doesn’t match the configured gateway IP address.
If an ARP address matches a configured gateway’s IP address, MAC address, and port list, then
bypass the Dynamic ARP Inspection (DAI) check no matter if the receiving port is ARP ‘trusted’ or
‘untrusted’.
Only physical ports and port channel interfaces are valid interface to be specified.
Example
This example shows how to configure an ARP spoofing prevention entry with an IP address of
10.254.254.251 and MAC address of 00-00-00-11-11-11 and activate the entry at port eth2/0/10 and
port channel 3.
Page 89
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
86
Switch#configure terminal
Switch(config)# ip arp spoofing-prevention 10.254.254.251 00-00-00-11-11-11
interface eth2/0/10
Switch(config)# ip arp spoofing-prevention 10.254.254.251 00-00-00-11-11-11
interface port-channel 3
Switch(config)#
6-2 show ip arp spoofing-prevention
This command is used to display the configuration of ARP spoofing prevention.
show ip arp spoofing-prevention
Parameters
None.
Default
None.
Command Mode
EXEC Mode or Any Configuration Mode.
Command Default Level
Level: 1.
Usage Guideline
Use this command to display all ARP spoofing prevention entries.
Example
This example shows how to display all ARP spoofing prevention entries.
Switch# show ip arp spoofing-prevention
IP MAC Interfaces
--------------- ----------------- ---------------------------
10.254.254.251 00-00-00-11-11-11 eth2/0/10
Total Entries: 1
Switch#
Display Parameters
IP
The IP address of the gateway.
MAC
The MAC address of the gateway.
Interfaces
The interfaces on which the ARP spoofing prevention is active.
Page 90
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
87
7. Asymmetric VLAN Commands
7-1 asymmetric-vlan
This command is used to enable the asymmetric VLAN function. Use the no form of this command to
disable the asymmetric VLAN function.
asymmetric-vlan
no asymmetric-vlan
Parameters
None.
Default
By default, this feature is disabled.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 12.
Usage Guideline
Use this command to enable or disable the asymmetric VLAN function.
Example
This example shows how to enable asymmetric VLAN.
Switch# configure terminal
Switch(config)# asymmetric-vlan
This example shows how to disable asymmetric VLAN.
Switch# configure terminal
Switch(config)# no asymmetric-vlan
Page 91
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
88
8. Authentication, Authorization, and
Accounting (AAA) Commands
8-1 aaa accounting commands
This command is used to configure the method list used for all commands at the specified privilege
level. Use the no form of this command to remove an accounting method list.
aaa accounting commands LEVEL {default | LIST-NAME} start-stop METHOD1 [METHOD2...]
no aaa accounting commands LEVEL {default | LIST-NAME}
Parameters
LEVEL
Specifies to do accounting for all configure commands at the
specified privilege level. Valid privilege level entries are 1 to 15.
default
Specifies to configure the default method list for accounting.
LIST-NAME
Specifies the name of the method list. This name can be up to 32
characters long.
METHOD1 [METHOD2...]
Specifies the list of methods that the accounting algorithm tries in
the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the aaa group server tacacs+ command.
none – Specifies no to perform accounting.
Default
No AAA accounting method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the method list for accounting of commands.
Example
This example shows how to create a method list for accounting of the privilege level of 15 using
TACACS+ and sends the accounting messages at the start and end time of access.
Switch#configure terminal
Switch(config)#aaa accounting commands 15 list-1 start-stop group tacacs+
Switch(config)#
8-2 aaa accounting exec
This command is used to configure the method list used for exec accounting for a specific line. Use
the no form of this command to disable the accounting exec.
Page 92
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
89
aaa accounting exec {default | LIST-NAME} start-stop METHOD1 [METHOD2...]
no aaa accounting exec {default | LIST-NAME}
Parameters
default
Specifies to configure the default method list for EXEC accounting.
LIST-NAME
Specifies the name of the method list. This name can be up to 32
characters long.
METHOD1 [METHOD2...]
Specifies the list of methods that the accounting algorithm tries in
the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server command.
none – Specifies not to perform accounting.
Default
No AAA accounting method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the method list for EXEC accounting.
Example
This example shows how to create a method list for accounting of user activities using RADIUS, which
will send accounting messages at the start and end time of access.
Switch#configure terminal
Switch(config)#aaa accounting exec list-1 start-stop group radius
Switch(config)#
8-3 aaa accounting network
This command is used to account user activity in accessing the network. Use the no form of this
command to remove the accounting method list.
aaa accounting network default start-stop METHOD1 [METHOD2...]
no aaa accounting network default
Parameters
network
Specifies to perform accounting of network related service requests.
start-stop
Specifies to send accounting messages at both the start time and
the end time of access. Users are allowed of access the network
regardless of whether the start accounting message enables the
Page 93
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
90
accounting successfully.
default
Specifies to configure the default method list for network
accounting.
METHOD1 [METHOD2...]
Specifies the list of methods that the accounting algorithm tries in
the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server command.
none – Specifies no to perform accounting.
Default
No AAA accounting method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the accounting method list for network access fees. For the default
method list to take effect, enable AAA first by using the aaa new-model command. The accounting
system is disabled if the default method list is not configured.
Example
This example shows how to enable accounting of the network access fees using RADIUS and sends
the accounting messages at the start and end time of access:
Switch#configure terminal
Switch(config)#aaa accounting network default start-stop group radius
Switch(config)#
8-4 aaa accounting system
This command is used to account system events. Use the no form of this command to remove the
accounting method list.
aaa accounting system default start-stop METHOD1 [METHOD2...]
no aaa accounting system default
Parameters
system
Specifies to perform accounting for system-level events.
start-stop
Specifies to send accounting messages at both the start time and
the end time of access. Users are allowed to access the network
regardless of whether the start accounting message enables the
accounting successfully.
default
Specifies to configure the default method list for system accounting.
METHOD1 [METHOD2...]
Specifies the list of methods that the accounting algorithm tries in
Page 94
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
91
the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server command.
none – Specifies no to perform accounting.
Default
No AAA accounting method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the accounting method list for system-events such as reboot, reset
events. For the default method list to take effect, enable AAA first by using the aaa new-model
command. The accounting system is disabled if the default method list is not configured.
Example
This example shows how to enable accounting of the system events using RADIUS and sends the
accounting messages while system event occurs:
Switch#configure terminal
Switch(config)# aaa accounting system default start-stop group radius
Switch(config)#
8-5 aaa authentication enable
This command is used to configure the default method list used for determining access to the
privileged EXEC level. Use the no form of this command to remove the default method list.
aaa authentication enable default METHOD1 [METHOD2...]
no aaa authentication enable default
Parameters
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
enable – Specifies to use the local enable password for
authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server command.
none - Normally, the method is listed as the last method. The user
Page 95
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
92
will pass the authentication if it is not denied by previous method
authentication.
Default
No AAA authentication method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the default authentication method list for determining access to the
privileged EXEC level when users issue the enable [privilege LEVEL] command. The authentication
with the RADIUS server will be based on the privilege level and take either “enable12” or “enable15”
as the user name.
Example
This example shows how to set the default method list for authenticating. The method tries the server
group “group2”.
Switch#configure terminal
Switch(config)# aaa authentication enable default group group2
Switch(config)#
8-6 aaa authentication dot1x
This command is used to configure the default method list used for 802.1X authentication. Use the no
form of this command to remove the default method list.
aaa authentication dot1x default METHOD1 [METHOD2...]
no aaa authentication dot1x default
Parameters
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
local – Specifies to use the local database for authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server.
none - Normally, the method is listed as the last method. The user
will pass authentication if it is not denied by previous method
authentication.
Default
No AAA authentication method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Page 96
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
93
Level: 15.
Usage Guideline
Use this command to configure the default authentication method list for 802.1X authentication.
Initially, the default method list is not configured. The authentication of 802.1X requests will be
performed based on the local database.
Example
This example shows how to set the default methods list for authenticating dot1X users.
Switch#configure terminal
Switch(config)# aaa authentication dot1x default group radius
Switch(config)#
8-7 aaa authentication jwac
This command is used to configure the default method list used for JWAC authentication. Use the no
form of this command to remove the default method list.
aaa authentication jwac default METHOD1 [METHOD2...]
no aaa authentication jwac default
Parameters
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
local – Specifies to use the local database for authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server.
none - Normally, the method is listed as the last method. The user
will pass authentication if it is not denied by previous method
authentication.
Default
No AAA authentication method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the default authentication method list for JWAC authentication. Initially,
the default method list is not configured. The authentication of JWAC requests will be performed
based on the local database.
Example
This example shows how to set the default methods list for authenticating dot1X users.
Page 97
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
94
Switch#configure terminal
Switch(config)#aaa authentication jwac default group radius
Switch(config)#
8-8 aaa authentication login
This command is used to configure the method list used for login authentication. Use the no form of
this command to remove a login method list.
aaa authentication login {default | LIST-NAME} METHOD1 [METHOD2...]
no aaa authentication login {default | LIST-NAME}
Parameters
default
Specifies to configure the default method list for login
authentication.
LIST-NAME
Specifies the name of the method list other than the default method
list. This name can be up to 32 characters long.
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
local – Specifies to use the local database for authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group tacacs+ - Specifies to use the servers defined by the
TACACS+ server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server command.
none - Normally, the method is listed as the last method. The user
will pass authentication if it is not denied by previous method’s
authentication.
Default
No AAA authentication method list is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the authentication method list used for login authentication. Multiple
method lists can be configured. The default keyword is used to define the default method list.
If authentication uses the default method list but the default method list does not exist, then the
authentication will be performed via the local database.
The login authentication authenticates the login user name and password, and also assigns the
privilege level to the user based on the database.
A method list is a sequential list describing the authentication methods to be queried in order to
authenticate a user. Method lists enable you to designate one or more security protocols to be used
for authentication, thus ensuring a backup system for authentication in case the initial method fails.
The switch system uses the first listed method to authenticate users. If that method fails to respond,
the switch system selects the next authentication method listed in the method list. This process
Page 98
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
95
continues until there is successful communication with a listed authentication method or all methods
defined in the method list are exhausted.
It is important to note that the switch system attempts authentication with the next listed authentication
method only when there is no response from the previous method. If authentication fails at any point
in this cycle, meaning that the security server or local username database responds by denying the
user access, the authentication process stops and no other authentication methods are attempted.
Example
This example shows how to set the default login methods list for authenticating of login attempts.
Switch#configure terminal
Switch(config)# aaa authentication login default group group2 local
Switch(config)#
8-9 aaa authentication mac-auth
This command is used to configure the default method list used for MAC authentication. Use the no
form of this command to remove the default method list.
aaa authentication mac-auth default METHOD1 [METHOD2...]
no aaa authentication mac-auth default
Parameters
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
local – Specifies to use the local database for authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server.
none - Normally, the method is listed as the last method. The user
will pass authentication if it is not denied by previous method
authentication.
Default
No AAA authentication method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the default authentication method list for MAC authentication. Initially,
the default method list is not configured. The authentication of MAC request will be performed based
on the local database.
Example
This example shows how to set the default methods list for authenticating mac-auth users.
Page 99
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
96
Switch#configure terminal
Switch(config)# aaa authentication mac-auth default group radius
Switch(config)#
8-10 aaa authentication web-auth
This command is used to configure the default method list used for Web authentication. Use the no
form of this command to remove the default method list.
aaa authentication web-auth default METHOD1 [METHOD2...]
no aaa authentication web-auth default
Parameters
METHOD1 [METHOD2...]
Specifies the list of methods that the authentication algorithm tries
in the given sequence. Enter at least one method or enter up to four
methods. The following are keywords that can be used to specify a
method.
local – Specifies to use the local database for authentication.
group radius – Specifies to use the servers defined by the RADIUS
server host command.
group GROUP-NAME – Specifies to use the server groups defined
by the AAA group server.
none - Normally, the method is listed as the last method. The user
will pass authentication if it is not denied by previous method
authentication.
Default
No AAA authentication method is configured.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to configure the default authentication method list for Web authentication. Initially,
the default method list is not configured. The authentication of the web-auth request will be performed
based on the local database.
Example
This example shows how to set the default method list for authenticating web-auth users.
Switch#configure terminal
Switch(config)# aaa authentication web-auth default group radius
Switch(config)#
8-11 aaa group server radius
This command is used to enter the RADIUS group server configuration mode to associate server
hosts with the group. Use the no form of this command to remove a RADIUS server group
aaa group server radius GROUP-NAME
Page 100
DGS-1510 Series Gigabit Ethernet SmartPro Switch CLI Reference Guide
97
no aaa group server radius GROUP-NAME
Parameters
GROUP-NAME
Specifies the name of the server group. This name can be up to 32
characters long. The syntax is a general string that does not allow
spaces.
Default
There is no AAA group server.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
Usage Guideline
Use this command to define a RADIUS server group. The created server group is used in the
definition of method lists used for authentication, or accounting by using AAA authentication and AAA
accounting command. Also use this command to enter the RADIUS group server configuration mode.
Use the server command to associate the RADIUS server hosts with the RADIUS server group.
Example
This example shows how to create a RADIUS server group with two entries. The second host entry
acts as backup to the first entry.
Switch#configure terminal
Switch(config)#aaa group server radius group1
Switch(config-sg-radius)# server 172.19.10.100
Switch(config-sg-radius)# server 172.19.11.20
Switch(config-sg-radius)# exit
Switch(config)#
8-12 aaa group server tacacs+
This command is used to enter the TACACS+ group server configuration mode to associate server
hosts with the group. Use the no form of this command to remove a TACACS+ server group
aaa group server tacacs+ GROUP-NAME
no aaa group server tacacs+ GROUP-NAME
Parameters
GROUP-NAME
Specifies the name of the server group. This name can be up to 32
characters long. The syntax is a general string that does not allow
spaces.
Default
There is no AAA group server.
Command Mode
Global Configuration Mode.
Command Default Level
Level: 15.
 Loading...