

Page 1
GPON ONT OFFICE
GPON ONT HOME
EN
Ref. 769501
User´s Manual
w w w . t e l e v e s . c o m
Ref. 769502
Page 2
Page 3
ENGLISH
EN
Índice
1. Summary .................................................................................................................................................................................................. 10
2. Technical Description ........................................................................................................................................................................... 11
2.1
Refs. 769501-769502 Gateway Main Functionalities ............................................................................................................... 11
2.2 Application Scenario ............................................................................................................................................................................ 11
2.3 Interoperability ....................................................................................................................................................................................... 12
2.4 Interfaces .................................................................................................................................................................................................. 13
2.5 General Features .................................................................................................................................................................................... 13
2.6 General Architecture............................................................................................................................................................................. 16
2.7 GPON .......................................................................................................................................................................................................... 16
2.8 Ethernet ..................................................................................................................................................................................................... 16
2.9 IPTV ............................................................................................................................................................................................................. 16
2.10 RF Video Overlay .................................................................................................................................................................................... 16
2.11 Voice ........................................................................................................................................................................................................... 17
2.12 WI-FI ............................................................................................................................................................................................................ 17
2.12.1 Operational description ...................................................................................................................................................................... 17
2.12.2 Block Diagram ......................................................................................................................................................................................... 18
2.12.3
Refs. 769501-769502 WI-FI Antennas ........................................................................................................................................... 19
2.13 Multiple QoS per VLAN ........................................................................................................................................................................ 19
2.14 Policing/Rate Limiting .......................................................................................................................................................................... 19
2.14.1 Downstream QoS ................................................................................................................................................................................... 19
2.14.2 Upstream QoS ......................................................................................................................................................................................... 19
2.14.3 Dynamic Bandwidth Allocation (DBA) ........................................................................................................................................... 20
2.14.4 Upstream QoS scenarios ..................................................................................................................................................................... 21
3. General Specications .......................................................................................................................................................................... 22
3.1 Interfaces .................................................................................................................................................................................................. 22
3.1.1 GPON .......................................................................................................................................................................................................... 22
3.1.2 Ethernet ..................................................................................................................................................................................................... 23
Page 4
4
GPON ONT
3.1.3 RF Overlay ................................................................................................................................................................................................. 23
3.1.4 FXS ............................................................................................................................................................................................................... 24
3.1.5 WI-FI ............................................................................................................................................................................................................ 25
3.2 General Features .................................................................................................................................................................................... 26
3.3 General Service Description ............................................................................................................................................................... 27
3.4 Optical metering .................................................................................................................................................................................... 28
3.5 Wavelength ltering ............................................................................................................................................................................. 28
3.6 GPON/Ethernet characteristics ......................................................................................................................................................... 28
3.7 GPON management .............................................................................................................................................................................. 29
3.8 Standards .................................................................................................................................................................................................. 30
4. Setup .......................................................................................................................................................................................................... 31
4.1 Before installing Refs. 769501-769502 device ............................................................................................................................. 31
4.2 Connections ............................................................................................................................................................................................. 31
4.3 How to Setup Refs. 769501-769502 ............................................................................................................................................... 33
4.4 Interface connection ............................................................................................................................................................................ 35
4.4.1 Optical cable connection .................................................................................................................................................................... 35
4.4.2 General Overview of Refs. 769501-769502 Connections ........................................................................................................ 35
5. Conguration .......................................................................................................................................................................................... 37
5.1
Refs. 769501-769502 activation ........................................................................................................................................................ 37
5.2 Customization ......................................................................................................................................................................................... 37
5.2.1 Software download from the OLT .................................................................................................................................................... 37
5.3 Network Setup ........................................................................................................................................................................................ 37
5.4 Refs. 769501-769502 General Management Conguration ................................................................................................... 38
5.5 Device Info................................................................................................................................................................................................ 39
5.5.1 Summary ................................................................................................................................................................................................... 40
5.5.2 WAN ............................................................................................................................................................................................................ 41
5.5.3 Statistics .................................................................................................................................................................................................... 42
5.5.4 Route .......................................................................................................................................................................................................... 45
5.5.5 ARP .............................................................................................................................................................................................................. 46
5.5.6 DHCP .......................................................................................................................................................................................................... 46
5.5.7 Voice ........................................................................................................................................................................................................... 47
5.6 Advanced Setup ..................................................................................................................................................................................... 48
5.6.1 Layer2 Interface ...................................................................................................................................................................................... 48
Page 5
EN
5
5.6.2 WAN Service/ ........................................................................................................................................................................................... 49
5.6.3 LAN .............................................................................................................................................................................................................. 78
5.6.4 NAT .............................................................................................................................................................................................................. 84
5.6.5 Security ...................................................................................................................................................................................................... 89
5.6.6 Parental Control ...................................................................................................................................................................................... 96
5.6.7 Quality of Service ................................................................................................................................................................................... 99
5.6.8 Routing ...................................................................................................................................................................................................... 104
5.6.9 DNS ............................................................................................................................................................................................................. 113
5.6.10 UPnP ........................................................................................................................................................................................................... 117
5.6.11 DNS Proxy ................................................................................................................................................................................................. 117
5.6.12 Storage Service ....................................................................................................................................................................................... 118
5.6.13 Interface Grouping ................................................................................................................................................................................ 118
5.6.14 IP Tunnel .................................................................................................................................................................................................... 120
5.6.15 Power Management ............................................................................................................................................................................. 124
5.6.16 Multicast .................................................................................................................................................................................................... 124
5.7 Wireless ...................................................................................................................................................................................................... 126
5.7.1 Basic ............................................................................................................................................................................................................ 126
5.7.2 Security ...................................................................................................................................................................................................... 128
5.7.3 MAC Filter.................................................................................................................................................................................................. 131
5.7.4 Advanced .................................................................................................................................................................................................. 132
5.7.5 Station Info ............................................................................................................................................................................................... 133
5.8 Voice ........................................................................................................................................................................................................... 133
5.8.1 SIP Basic Settings ................................................................................................................................................................................... 134
5.8.2 SIP Advanced Settings ......................................................................................................................................................................... 137
5.8.3 SIP Debug Settings ................................................................................................................................................................................ 140
5.9 Diagnostics ............................................................................................................................................................................................... 141
5.10 Management ........................................................................................................................................................................................... 141
5.10.1 Settings ...................................................................................................................................................................................................... 142
5.10.2 System Log ............................................................................................................................................................................................... 144
5.10.3 Security Log ............................................................................................................................................................................................. 147
5.10.4 TR-069 Client ........................................................................................................................................................................................... 148
5.10.5 Internet Time ........................................................................................................................................................................................... 150
5.10.6 Access Control ......................................................................................................................................................................................... 152
Page 6
6
GPON ONT
5.10.7 Update Software .................................................................................................................................................................................... 153
5.10.8 Reboot ....................................................................................................................................................................................................... 154
5.11 Logout ........................................................................................................................................................................................................ 154
6. Operation Indicators ............................................................................................................................................................................. 155
6.1 Refs. 769501-769502 ........................................................................................................................................................................... 155
6.1.1 LED Indicators Status ............................................................................................................................................................................ 155
6.1.2 Troubleshooting ..................................................................................................................................................................................... 157
7. CLI ................................................................................................................................................................................................................ 158
7.1 Overview ................................................................................................................................................................................................... 158
7.2 Nodes and Commands ........................................................................................................................................................................ 158
7.2.1 “wan” node ............................................................................................................................................................................................... 158
7.2.2 “lan” node .................................................................................................................................................................................................. 163
7.2.3 “nat” node ................................................................................................................................................................................................. 166
7.2.4 “dns” node ................................................................................................................................................................................................. 170
7.2.5 “qos” node ................................................................................................................................................................................................. 172
7.2.6 “voice” node ............................................................................................................................................................................................. 176
7.2.7 “security” node ........................................................................................................................................................................................ 178
7.2.8 “routing” node ......................................................................................................................................................................................... 180
7.2.9 “multicast” node ..................................................................................................................................................................................... 182
7.2.10 “diagnostics” node ................................................................................................................................................................................. 183
7.2.11 “arp” node ................................................................................................................................................................................................. 184
7.2.12 “device-info” node ................................................................................................................................................................................. 184
7.2.13 “statistics” node ....................................................................................................................................................................................... 185
7.2.14 “dhcp” node .............................................................................................................................................................................................. 185
7.2.15 “upnp” node ............................................................................................................................................................................................. 186
7.2.16 “intf-grouping” node ............................................................................................................................................................................. 186
7.2.17 “management” node ............................................................................................................................................................................ 188
7.3 VoIP conguration using CLI.............................................................................................................................................................. 192
7.3.1 IPoE Service Conguration ................................................................................................................................................................. 192
7.3.2 VoIP Conguration ................................................................................................................................................................................ 193
Page 7
EN
7
Glossary of Acronyms and Denitions
Acronyms and abbreviations
3G Third generation mobile telecommunications
AAA Authentication, Authorization, and Accounting
AC Alternating Current
AC Access Concentrator
ACL Access Control List
ACS Auto Conguration Server
AES Advanced Encryption Standard
ARP Address Resolution Protocol
AS Autonomous System
AUTO-MDIX Medium Dependent Interface Crossover Automatic Choice
BBF Broadband Forum
BGP Border Gateway Protocol
CAT5E Category 5 Cable
CATV Cable TV
CIFS Common Internet File System
CLI Command-line interface
CO Central Oce
CPE Customer-Premises Equipment
CRC Cyclic Redundancy Check
DC Direct Current
DDNS Dynamic DNS
DHCP Dynamic Host Conguration Protocol
DNS Domain Name System
DSCP Dierentiated Services Code Point
DSL Digital Subscriber Line
EAP-SIM Extensible Authentication Protocol Method for GSM Subscriber Identity Module
FTP File Transfer Protocol
FTTH Fiber-To-The-Home
FXS Foreign eXchange Station
GbE Gigabit Ethernet
GEM GPON Encapsulation Module
GEPON Gigabit Ethernet Passive Optical Network
GPON Gigabit-capable Passive Optical Network
GSM Global System for Mobile Communications
GW Gateway
HG Home Gateway
HSI High Speed Internet
ID Identication
IEEE Institute of Electrical and Electronics Engineers
IGMP Internet Group Management Protocol
IMS IP Multimedia Subsystem
IP Internet Protocol
Page 8
8
GPON ONT
IPTV Internet Protocol Television
IPv4 Internet Protocol version 4
IPv6 Internet Protocol version 6
ISP Internet Service Provider
ITU-T Telecommunications International Telecommunication Union
L2 OSI Layer 2
L3 OSI Layer 3
LAN Local Area Network
LED Light Emitting Diode
MAC Media Access Control
MAN Metropolitan Area Network
MAP Mobile Application Part
ME Managed Entity
MEGACO Media Gateway Control Protocol
MRU Maximum Receive Unit
MTBF Mean Time Between Failures
NAS Network Access Server
NAT Network Address Translation
NGN Next Generation Network
NMS Network Management System
OLT Optical Line Terminal
OMCI ONT Management Control Interface
ONT Optical Network Terminal
OPEX Operational Expenditure
OSI Open Systems Interconnection
PC Personal Computer
PON Passive Optical Network
PPP Point-to-Point Protocol
PPPoE Point-to-Point Protocol over Ethernet
PSK Phase-Shift Keying
PWLAN Public Wireless LAN
QoS Quality of Service
RADIUS Remote Authentication Dial In User Service
RF Radio Frequency
RGW Residential Gateway
RIP Routing Information Protocol
RJ11 Registered Jack model 11
RJ45 Registered Jack model 45
SAMBA SMB/CIFS implementation
SC/APC SC/APC optical connector
SIM Subscriber Identity Module
SIP Session Initiation Protocol
SIP Session Initiation Protocol
SMB Server Message Block
SNTP Simple Network Time Protocol
SS7 Signalling System No. 7
Page 9
EN
9
SSID Service Set IDentier
STB Set Top Box
SW Software
T-CONT Transmission Container
TCP Transmission Control Protocol
TDM Time Division Multiplexing
TDMA Time Division Multiple Access
TKIP Temporal Key Integrity Protocol
TR-069 Technical Report 069
TTL Time to Live
TV Television
UDP User Datagram Protocol
URL Uniform Resource Locator
USB Universal Serial Bus
UTP Unshielded Twisted Pair
VAD Voice Activity Detection
VAP Virtual Access Point
VID VLAN Identier
VLAN Virtual Local Area Networks
VoIP Voice over Internet Protocol
VPN Virtual Private Network
WAN Wide Area Network
WEP Wired Equivalent Privacy
WI-FI Wireless Fidelity
WLAN Wireless Local Area Network
WPA Wi-Fi Protected Access
WPS WI-FI Protected Setup
xBASE-T Ethernet over twisted pair technologies
Page 10
10
GPON ONT
1. Summary
The Refs. 769501-769502 is an Optical Terminal Equipment (ONT) unit for Passive Optical Networks (PON) termination in a FTTH (Fiber-To-TheHome) service delivery architecture . Refs. 769501-769502 communicates with the OLT (Optical Line Terminal) for the PON side and with the
customer’s premises for the client side. This equipment supports triple-play services - high speed internet (HSI), voice (VoIP), video (IPTV and RF
Overlay) and WPS (WI-FI Protected Setup). The use of the GPON ber access technology does allow a signicant service delivery increase when
compared with traditional xDSL technologies.
The Refs. 769501-769502 equipment technology is based on GEM (GPON Encapsulation Method), and complies with ITU-T G.984.x. recommendation as like as G.984.4 (OMCI) ensuring interoperability with major GPON OLT vendors (BBF.247).
These base functionalities, together with the support for bit rates of up to 2.5 Gbps (downstream) and 1.24 Gbps (upstream), an optical network
splitting ratio of up to 1:64 in a single ber and a distance range of up to 60 km, make the GPON technology and the Refs. 769501-769502 the most
ecient option for passive optical network topologies, when integrated service delivery is an issue.
Together with multi-vendor OLT interoperability (BBF.247 certied), other dierentiated features of the Refs. 769501-769502 product are the
embedded RF Video Overlay as well as the chance to have several TV channel packs by means of using remote managed analog RF video overlay
lters. The use of an embedded optical reective component also increases probing resolution in case of FTTH probing. The Refs. 769501-769502
is also one of the rst single household integrated CPE solution (ONT+GATEWAY).
As opposed to the point-to-point architecture, in which there is one physical port per client in the Central Oce, in GPON point-to-multipoint
architecture there is only a single laser and photo-detector in the Central Oce (CO) to serve up to 64 CPEs. All the Optical Distribution Network
is built by means of passive equipment modules with a long live MTBF standards and very low OPEX.
Page 11
EN
11
2. Technical Description
2.1 Refs. 769501-769502 Gateway Main Functionalities
The Refs. 769501-769502 Gateway is aimed for customer premises and complies with the ITU-T G.984.x recommendation in order to transport
(over GPON) and deliver (to premises domain) the full broadband service pack.
Broadband service applications are commonly referred as below:
High speed internet (HSI);
Voice (VoIP) services (SIP/MEGACO H.248);
TV (whether IPTV or analog RF video overlay);
WI-FI.
The multiplay environment is thus reinforced when combining the upper referred services.
2.2 Application Scenario
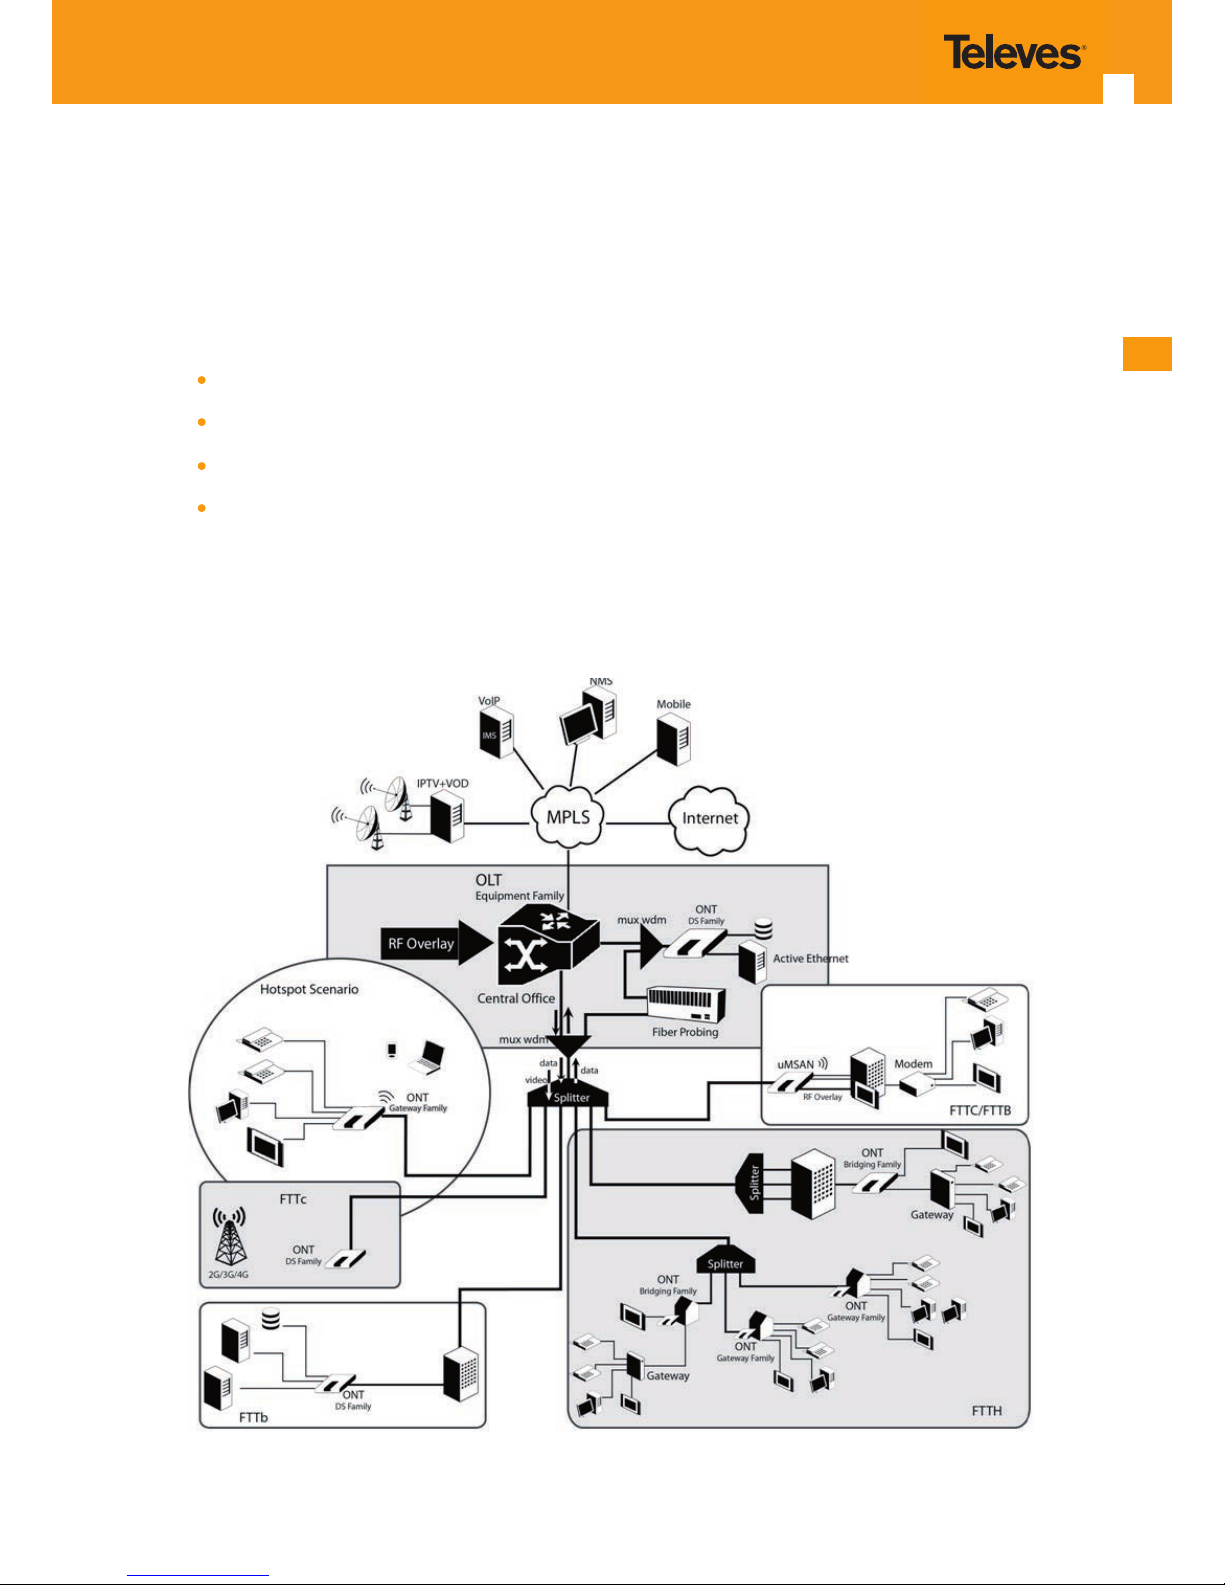
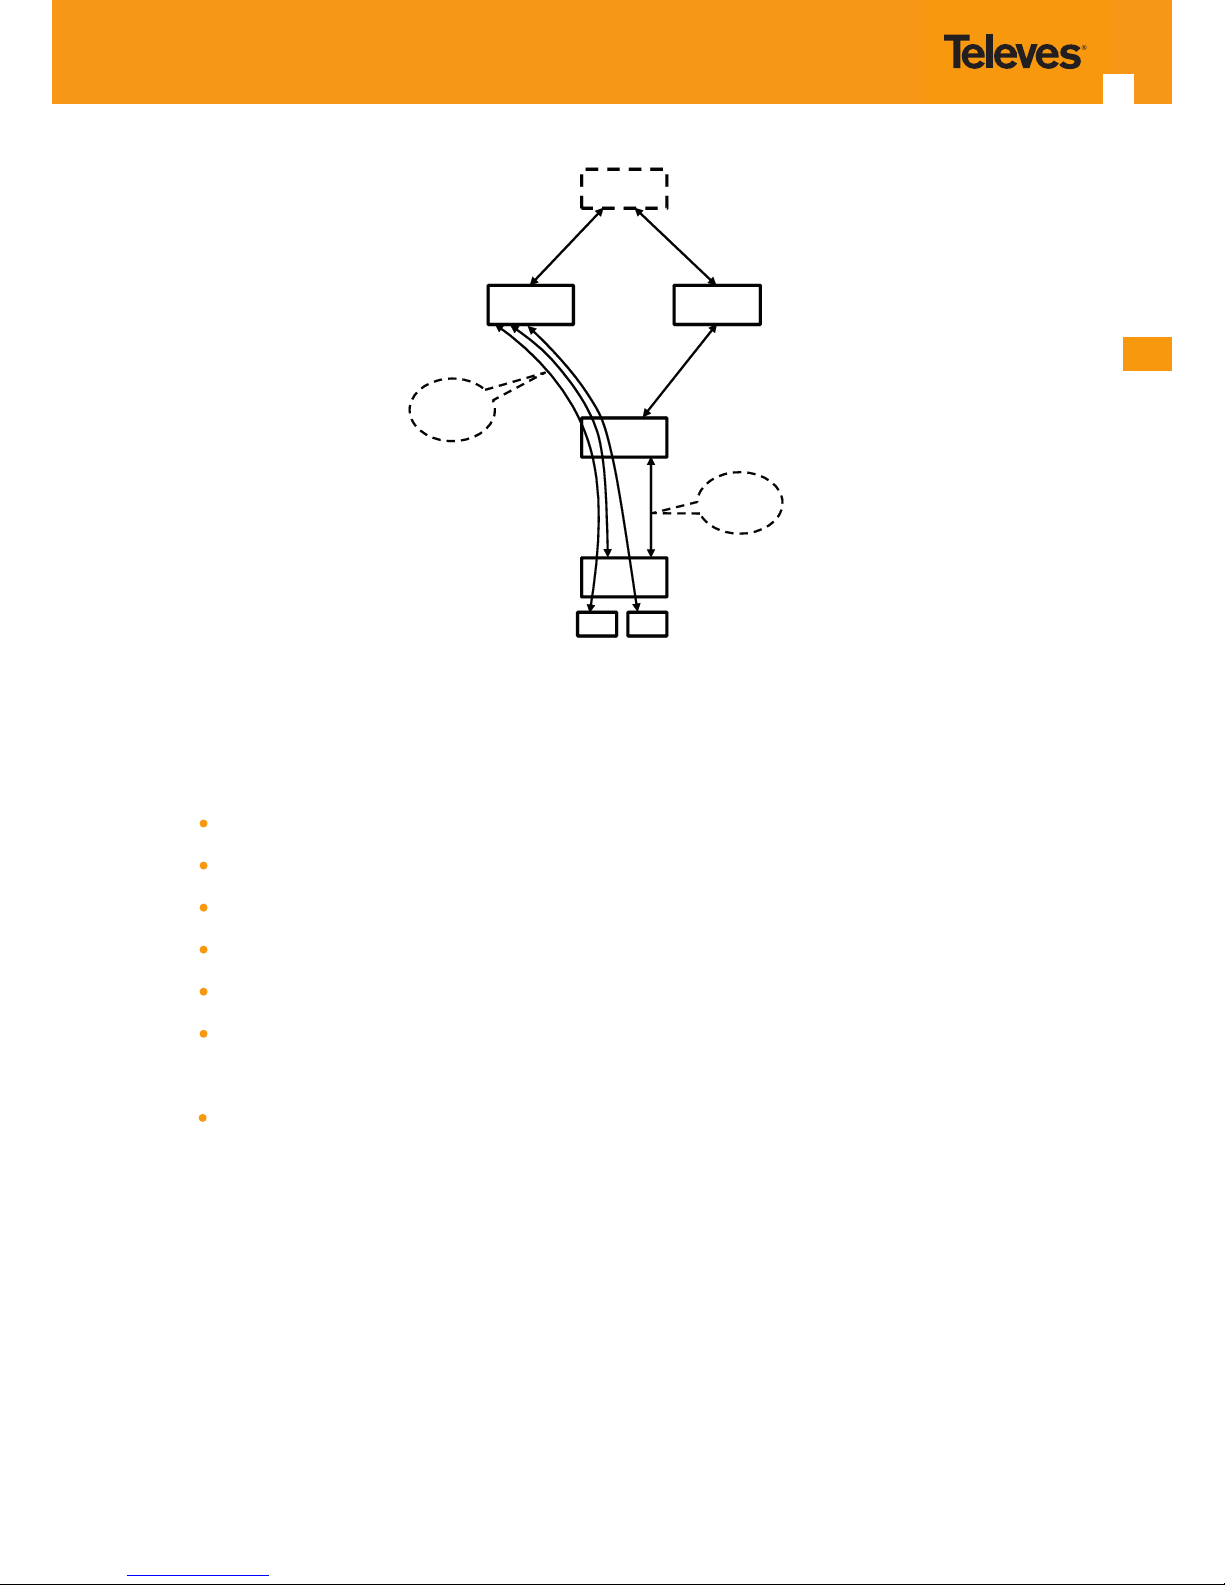
The next gure shows a possible gateway scenario for Refs. 769501-769502 equipments when in an end-to-end PON architecture.
Figure 2-1: Refs. 769501-769502 equipment application scenario
Page 12
12
GPON ONT
2.3 Interoperability
The ONT gateway family equipment complies with ITU-T G.984.x. Recommendation as like as G.984.4 (OMCI) ensuring multi-vendor OLT interoperabily with major GPON OLT vendors, as dened in BBF.247 ONU certication program.
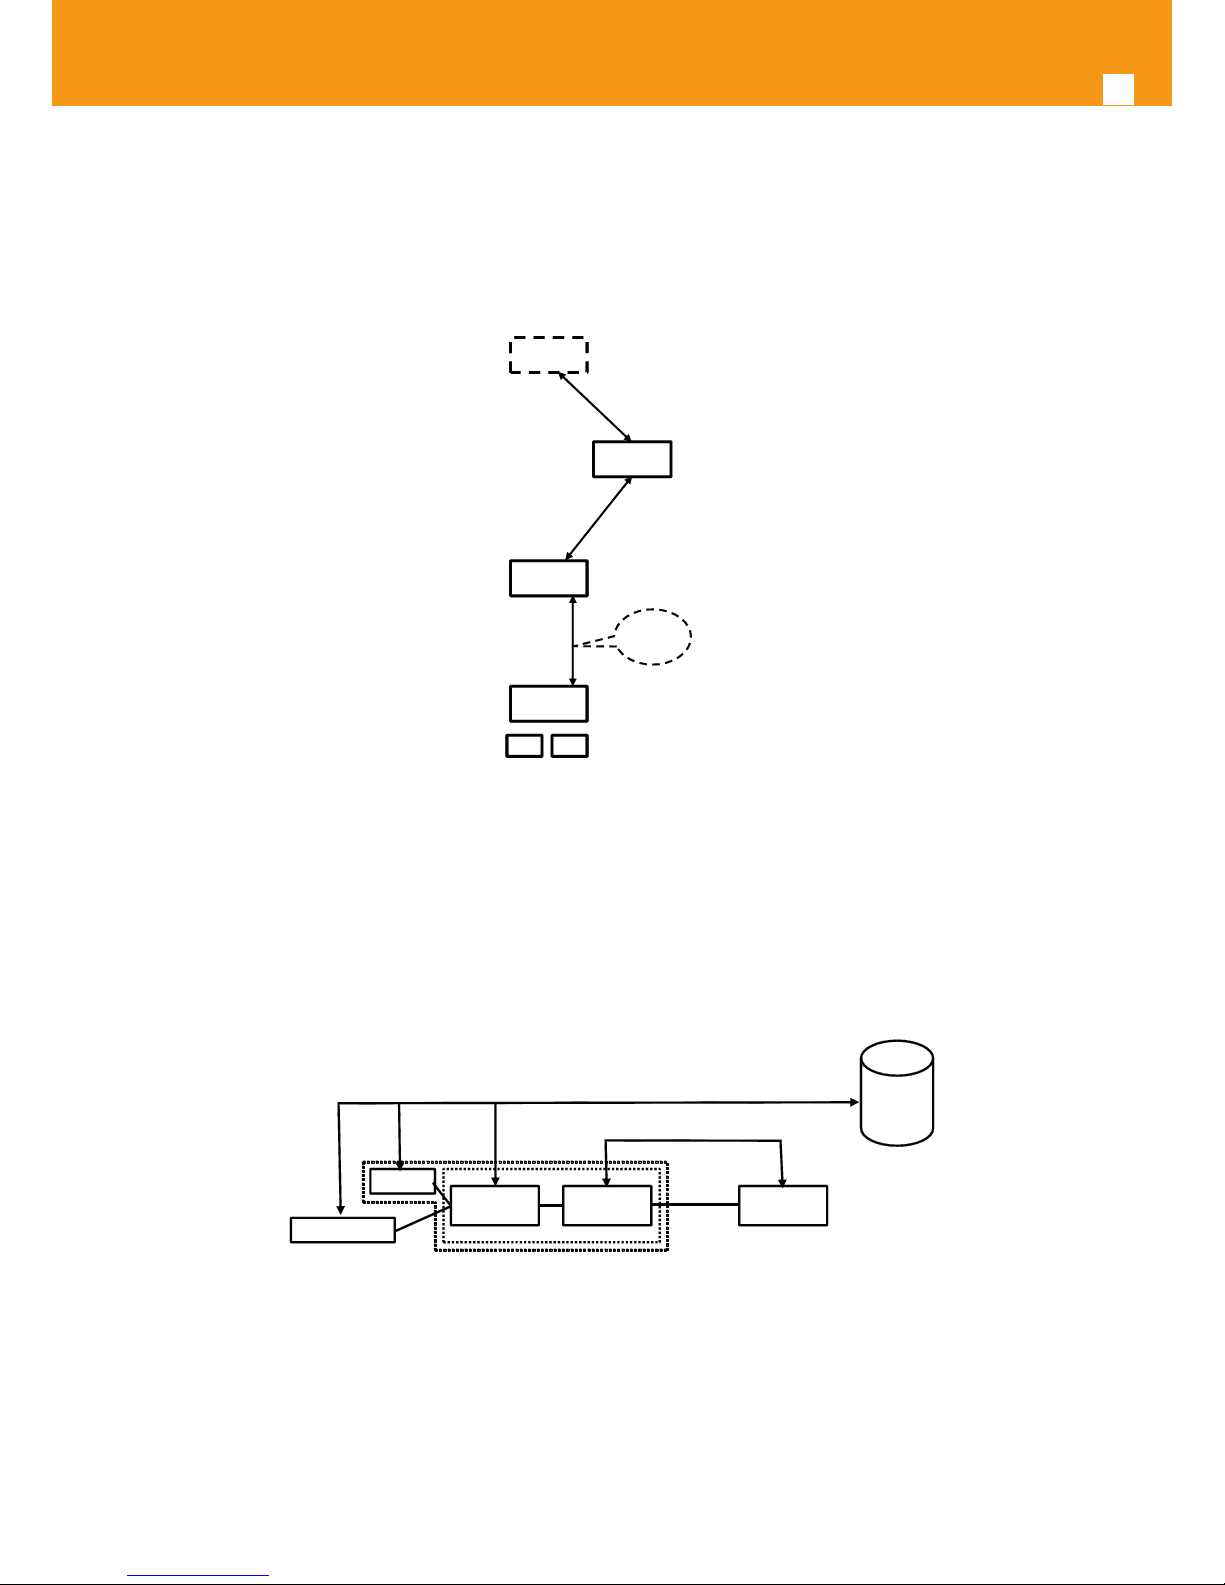
BBF.247 ONU certication program certies ONT link layer conguration and management protocol, OMCI, Figure 2-2, as dened by ITU-T G.984.3,
ITU-T G.984.4 and ITU-T G.988.
OSS
EMS
OLT
ONT
RGW STB
OMCI
Network Topology
OLT/ONT
Management
(TL1, SNMP)
Figure 2-2: Link Layer Conguration and Management
IP-based services conguration and management is achieved by means of the TR-069 protocol as dened by Broadband Forum. This procedure
takes for granted that previously the link layer connectivity has been achieved.
TR-069 is then transparent to the OLT, since the TR-069 connections are established between the ACS and the ONTs, Figure 2-4.
ONT gateway family equipments integrate gateway functionalities. Link layer conguration and management is achieved by the use of OMCI,
while IP-based services (RG functionality and Voice over IP) are congured and managed by TR-069, Figure 2-3.
ONTRG OLT
ACS
VoIP
Terminal
TR-069
OMCI
Figure 2-3: ONT gateway family equipment conguration
Page 13
EN
13
OSS
EMS
OLT
ONT
RGW STB
ACS
TR069
OMCI
Network TopologySubscriber Service
OLT/ONT
Management
(TL1, SNMP)
Figure 2-4: IP Based services-TR069 conguration
2.4 Interfaces
Client interface options are of type:
4x 100/1000Base-T for Ethernet network connection (RJ45 connectors);
2x FXS channels (RJ11 connectors);
2x2 @ 2.4/5.0 GHz wireless interfaces (802.11 b/g/n);
2x USB 2.0 Masters for printer sharing, media sharing and for 3G/4G backup uplink;
RF Overlay interface;
Control switches for power and WI-FI;
Network interface option is of type:
GPON SC/APC Optical connector (B+/C+).
2.5 General Features
GPON is a point-to-multipoint passive optical network, in which unpowered optical splitters are used to enable a single optical ber to serve
multiple premises, typically 1-64.
A PON consists of an optical line terminal (OLT) at the central oce and a number of optical network terminals (ONT) at the customer premises.
Downstream signals are broadcasted to all premises sharing multiple bers. Encryption can prevent eavesdropping. Upstream signals are combined using a multiple access protocol (Time Division Multiple Access- TDMA). The OLT queues data to the various ONT terminals in order to provide time slot assignments for upstream communication.
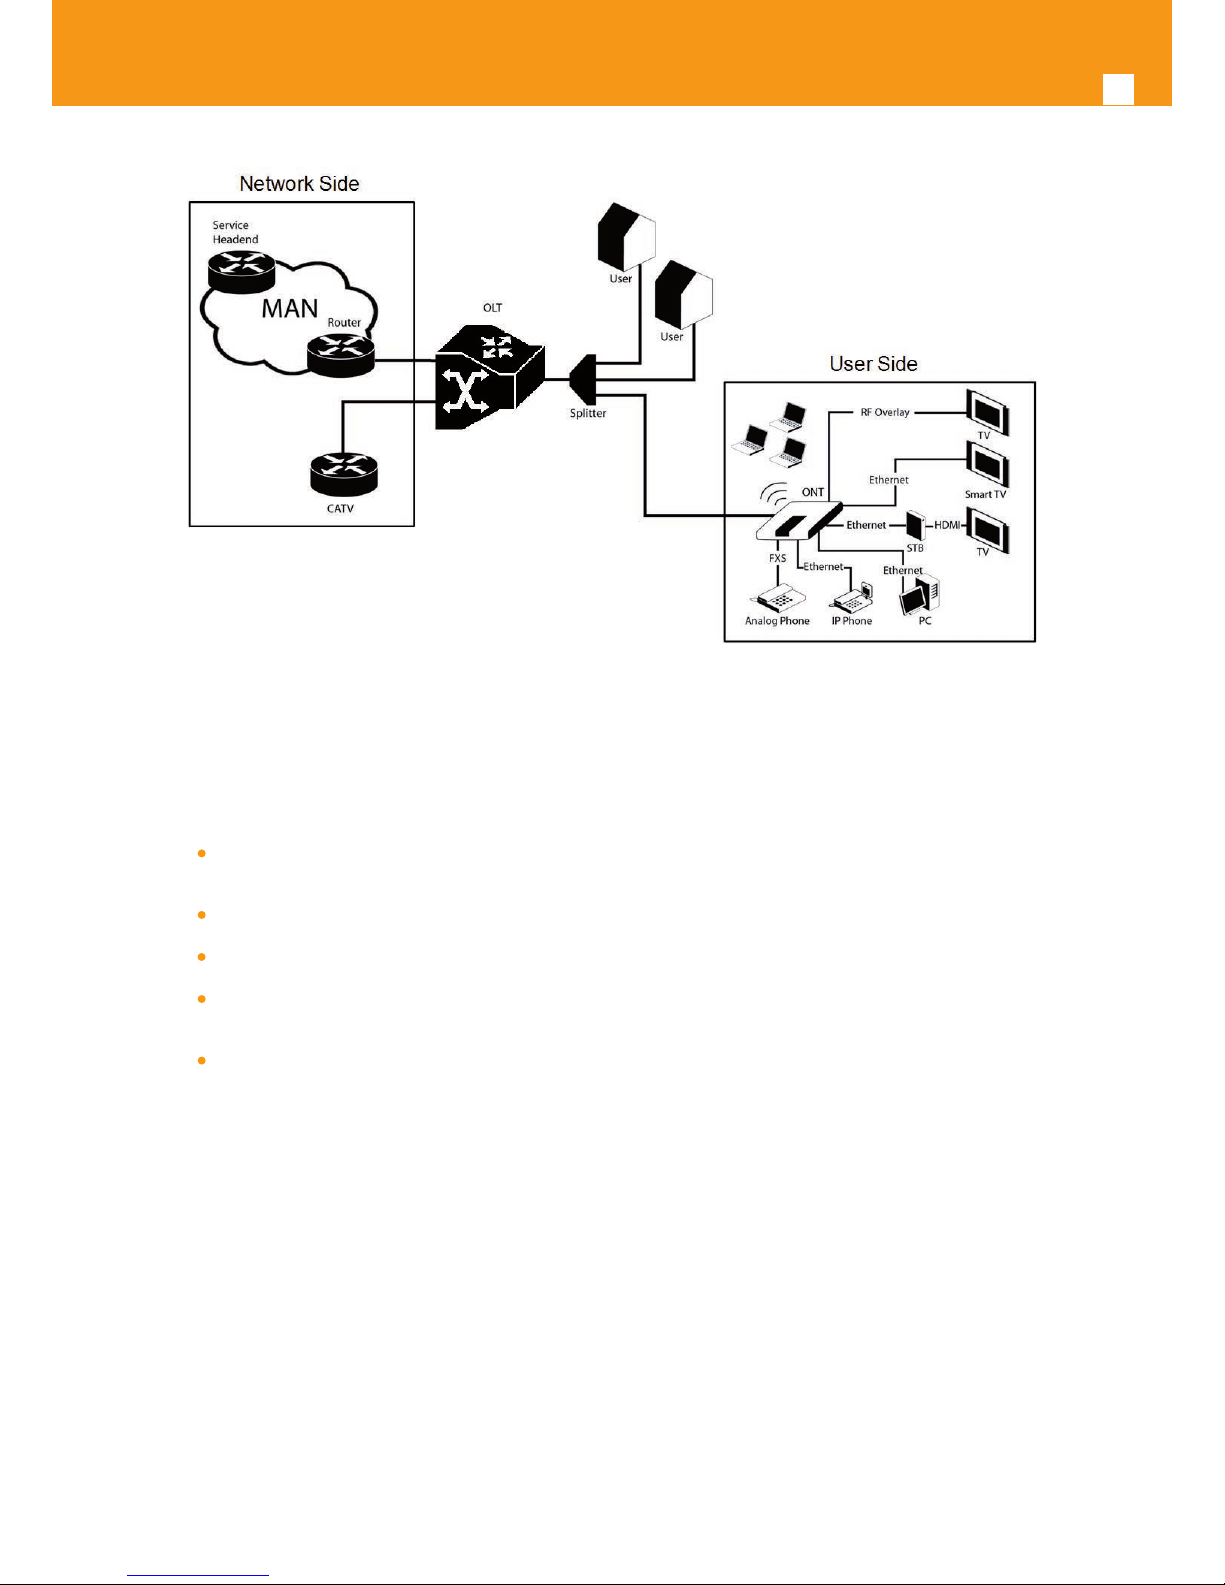
In Figure 2-5 it is shown a scenario for a multi-service user domain basic architecture through an ISP network.
Page 14
14
GPON ONT
Figure 2-5: Optical ber Internet service user access
In the upstream direction, the Refs. 769501-769502 is connected to the optical splitter and respectively to the OLT through the PON port to provide integrated access services through the service headend.
In the downstream direction, the Refs. 769501-769502 is connected to various terminals through the following LAN-side ports to implement
multi-play services:
Four 10/100/1000M Base-T Ethernet ports, which can be connected to terminals such as PCs, STBs, and video phones to provide
the high-speed data and video services;
Two FXS ports, which can be connected to telephone sets to provide VoIP services;
Two Wi-Fi antennas, which can connect to Wi-Fi terminals wirelessly to provide a secure and reliable high-speed wireless network;
Two USB ports, which can be connected to a USB storage device to provide convenient storage and le sharing services within a
home network;
One RF Overlay port, which can be connected to a TV set to provide high-quality CATV service.
The communication between client equipment (ONT) and the ISP access routers (MAN edge) is made by an optical ber-based passive architecture (ITU-T G.984 Recommendation). The GPON network acts as a Layer 2 Ethernet metropolitan network. Access network assures and controls
the media (MAC) communication through a TDMA scheme, introducing GEM (GPON Encapsulation Method) in between to adapt TDM layer to
Ethernet.
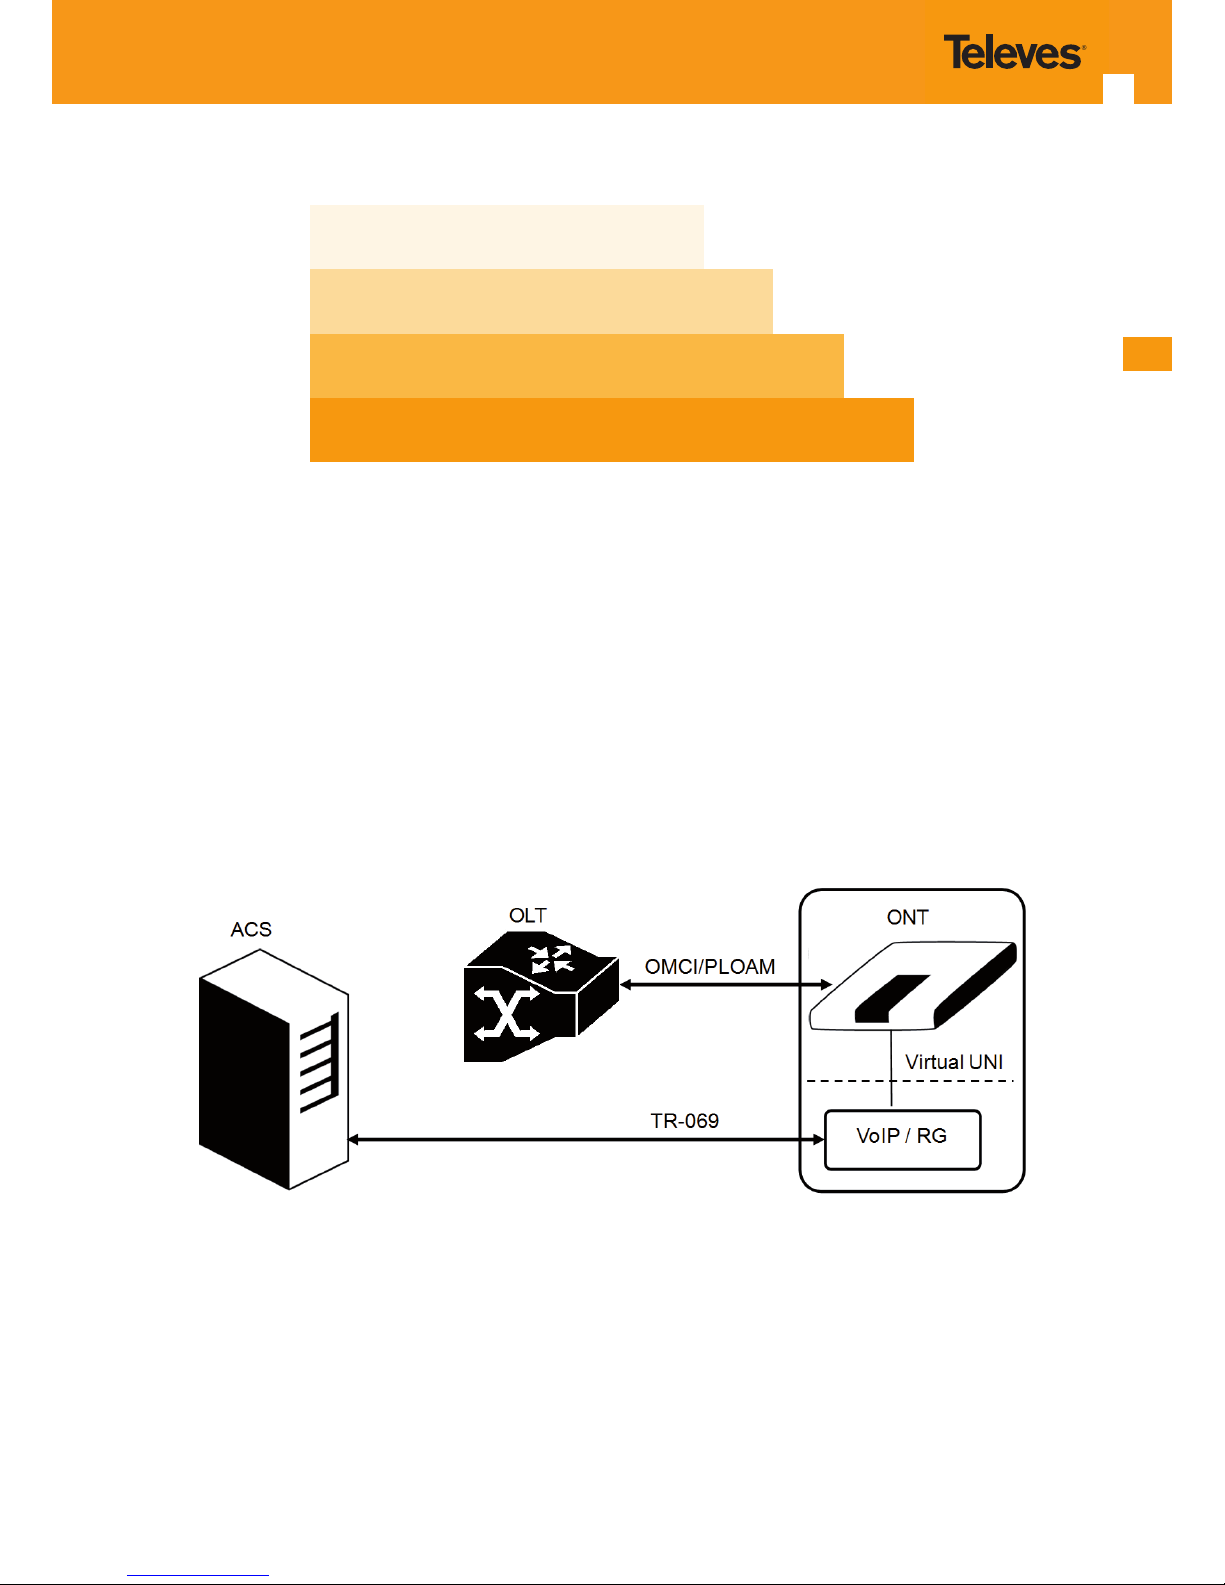
The used protocol stack is shown in Figure 2-6.
Page 15
EN
15
IP
ETHERNET
GEM
TDM/TDMA
Figure 2-6: Stack of protocols for GPON architecture
Several transmission containers (T-CONT) are assigned to each user. Each T-CONT has an associated GEM port and each GEM port has a VLAN
identier and an 802.1p priority level.
The ONT classies the trac depending on the VLAN and the marked priority, and routes it over the corresponding T-CONT/GEM port. Thus for
frame multiplexing, GEM and T-CONT ports are used for uplink while the downlink only use the GEM ports feature.
ONT7-RGW complies with Broadband Forum TR-142 Technical Report, which denes a framework for the remote conguration and management
of IP-based services over PON (Passive Optical Network) and ber access technology.
TR-142 framework uses TR-069 which is the protocol of choice for the remote management and conguration of IP services over PON and ber
access networks. TR-069 is intended to be used for the remote conguration and management of IP services running over ONT, as well as for some
aspects of ONT management.
Figure 2-7: TR-142 Framework
TR-142 framework denes a virtual UNI between the OMCI (ONT Management Control Interface) and TR-069 management domains.
This framework allows PON CPE with L3 layer capabilities to be mass remotely congured, troubleshoot and managed by an ACS (Auto Conguration Server) using TR-069 CPE WAN Management Protocol.
Page 16
16
GPON ONT
2.6 General Architecture
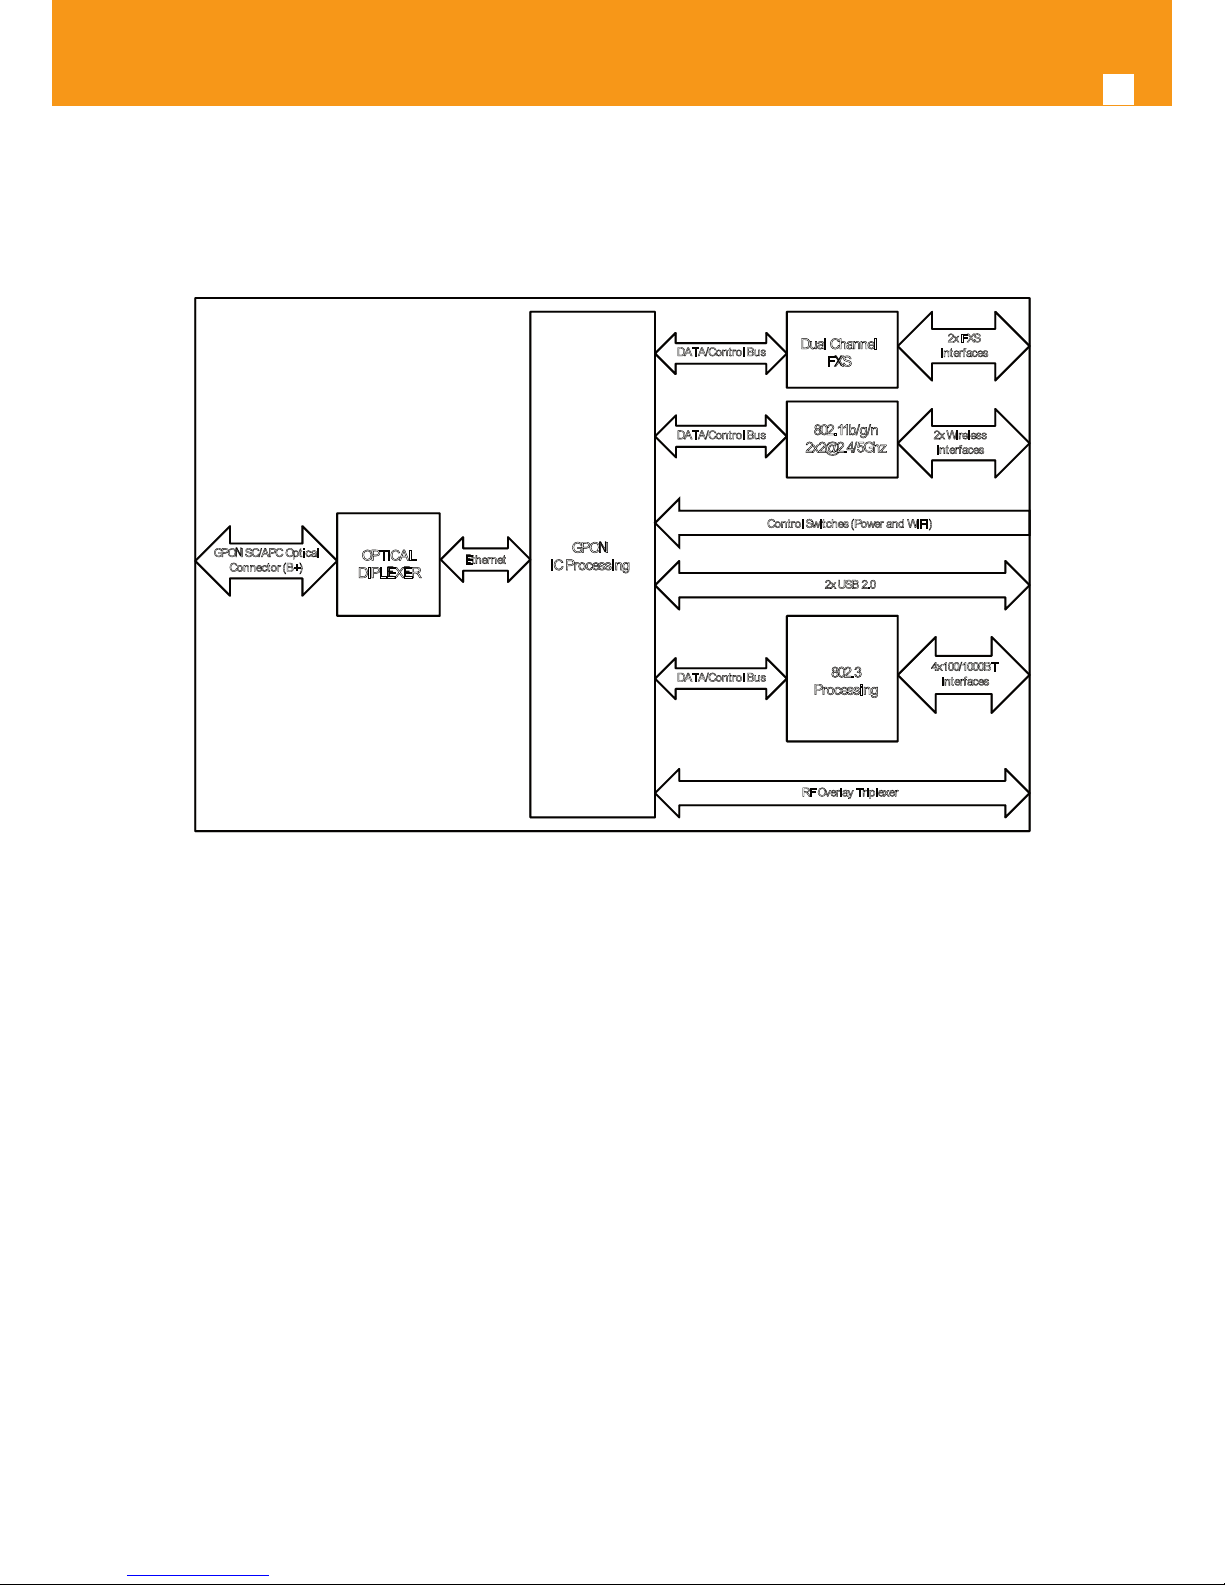
The Refs. 769501-769502 basic system architecture is hereafter presented.
OPTICAL
DIPLEXER
Dual Channel
FXS
802.11b/g/n
[email protected]/5Ghz
802.3
Processing
GPON
IC Processing
DATA/Control Bus
DATA/Control Bus
DATA/Control Bus
2x FXS
Interfaces
2x Wireless
Interfaces
4x100/1000BT
Interfaces
Ethernet
GPON SC/APC Optical
Connector (B+)
RF Overlay Triplexer
2x USB 2.0
Control Switches (Power and WiFi)
Figure 2-8: Refs. 769501-769502 system architecture
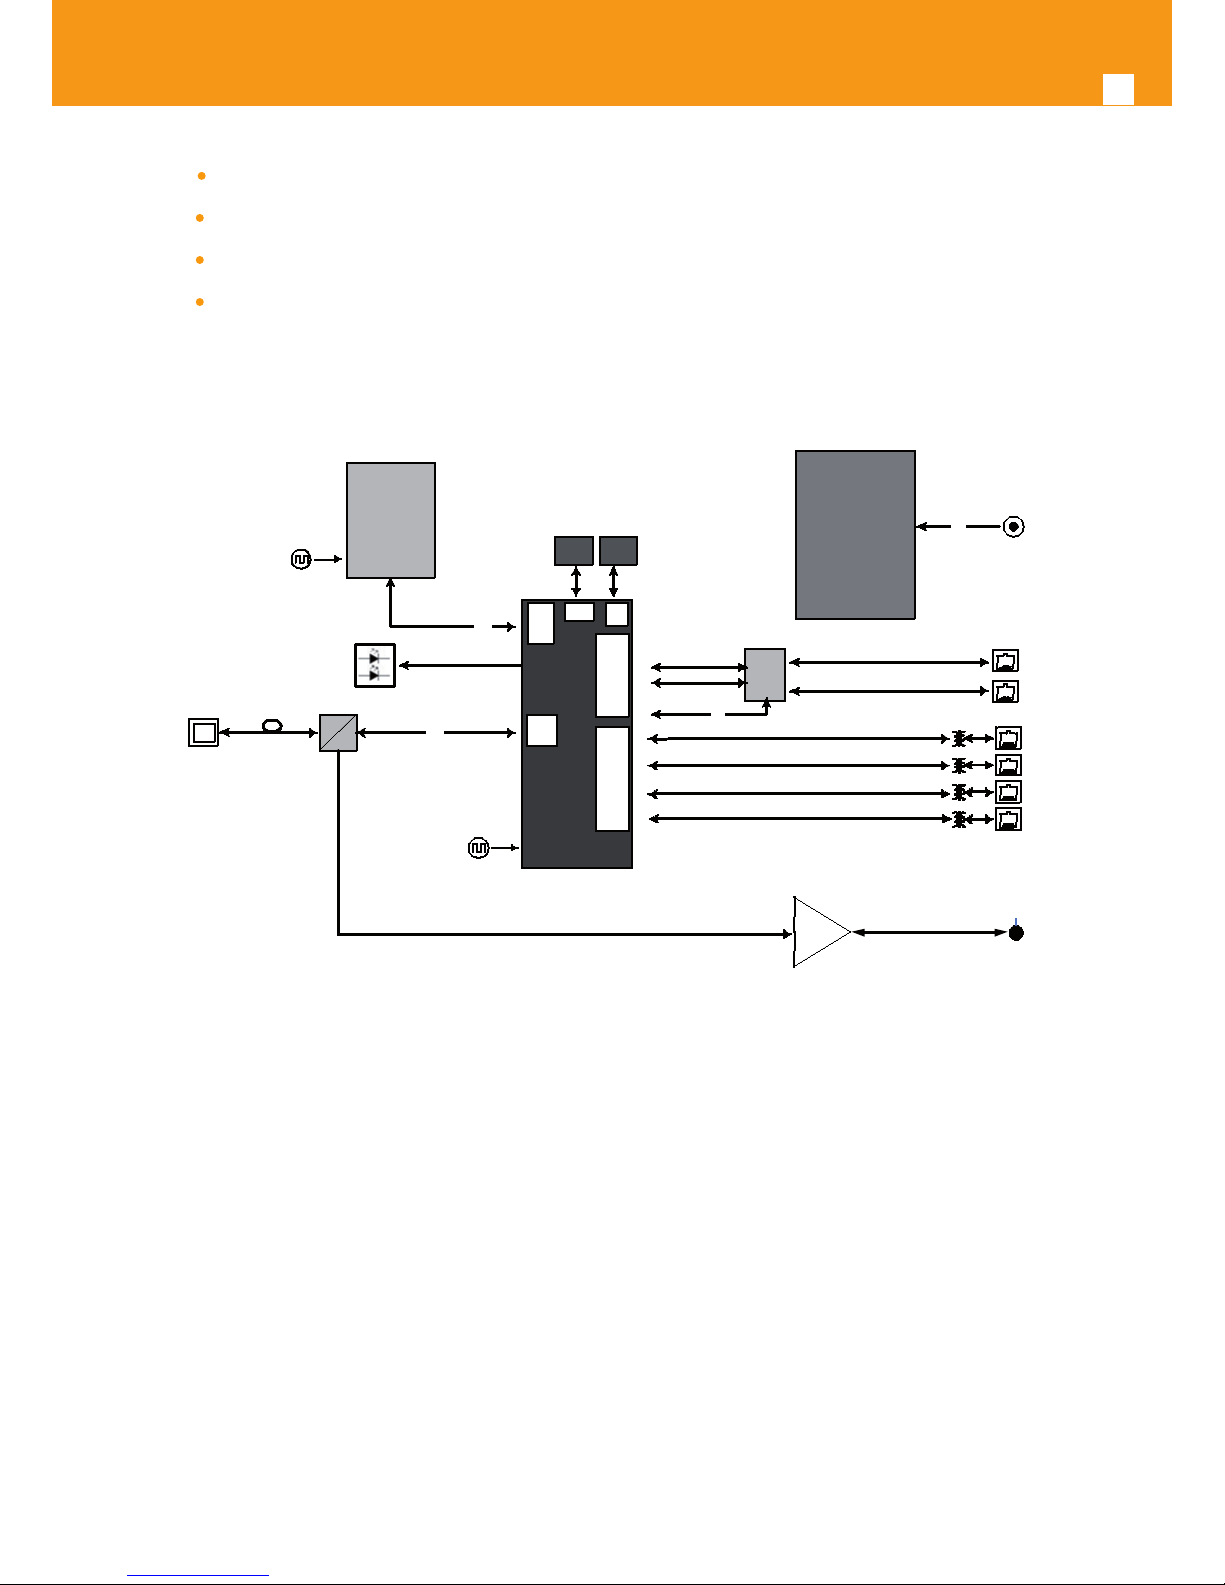
The GPON IC Processing unit is the core component inside Refs. 769501-769502. It is responsible for the interconnection and processing between
client side interfacing and optical GPON Uplink interface.
2.7 GPON
The Refs. 769501-769502 GPON layer as G.984.x uses 1490nm downstream and 1310nm upstream of the optical wavelengh, with 2,488Gbps
downstream and 1,244Gbps upstream by using an SC/APC protected optical connector.
2.8 Ethernet
Ethernet is the wired LAN technology and is revised in the IEEE 802.3 standard. At the OSI reference system, Ethernet is at the Data Link layer. In
the Refs. 769501-769502 equipment both WAN and LAN type of physical interfaces are 10/100/1000BASE-T AUTO-MIX Ethernet type over RJ45
conectors.
2.9 IPTV
For the IPTV service the Refs. 769501-769502 also behaves like a Layer 2 bridging device. For this service, the Refs. 769501-769502 has a specic
GEM PORT for Multicast. This same GEM PORT is requested by the user in order to have access to the various IPTV channels. Every time a user
requests a new channel, the Refs. 769501-769502 will send to OLT a IGMP packet requesting that Channel. The Refs. 769501-769502 is also responsible for implementing the snooping for the channels that the user requests.
2.10 RF Video Overlay
Broadcast video signal travels over ber from the central oce in the 1550nm wavelength and is demuxed and converted in the Refs. 769501769502 to a F conector (75 Ohm) RF Overlay interface to deliver a RF TV signal going from 47MHz up to 862MHz bandwidth. Refs. 769501-769502
may also implement multiple analog ltering on the RF Interface in order to turn the open RF Spectrum in a group of sliced TV channel packs that
are remotely enabled from the NMS.
Page 17
EN
17
PON RF video overlay service is the way to deliver a broadcast TV service over a PON ber network. This video overlay service is foreseen to provide
mainly broadcast video transmission in contrast to unicast and/or multicast IP video transmission which is used for IPTV and/or Video-On-Demand
having the need for a Set-Top-Box or a Smart TV at the customer premises.
Standardization bodies (ITU for GPON and IEEE for GEPON) have excluded the use of the 1550 -1560nm wavelength window for IP transmission on
PONs and have even continued with this approach for the upcoming 10GPON and 10GEPON standards. The 1550-1560nm wavelength window
is thus exclusively reserved for the video overlay transmission and by that mean an option to ooad unicast and/or multicast video transmission
from the IP PON transmission link.
Typically an extra ber testing signal (1650nm) for optical network probing is also added to the PON optical communication link.
2.11 Voice
Refs. 769501-769502 voice service provisioning could be made through OLT congurations over OMCI messages or could be downloaded (FTP)
from the OLT up to the Refs. 769501-769502 after the Refs. 769501-769502 registration on the PON network. The Refs. 769501-769502 gateway
family equipments have the ability to deliver the Voice service over two types of interface:
Logical interface (VLAN encapsulation)
If the Refs. 769501-769502 has no FXS ports and the VoIP service is transparently forwarded from the OLT up to the Home Gateway (and vice versa)
within a previously dened voice VLAN. Refs. 769501-769502 respects the dened priority and implements the trac encapsulation from its own
Ethernet interface into a specic T-CONT/GEM-Port over the PON interface and up to the OLT equipment.
Physical interface (FXS ports)
The Refs. 769501-769502 has physical RJ11 FXS interfaces. In this version of the Refs. 769501-769502 equipment, voice interfaces are terminated in
the equipment by means of FXS (RJ11) connections. The RJ11 analog terminals adapter function is auto/self-congured, integrated (analog/VoIP)
and associated with a dened SIP or Megaco (H.248) user.
The Refs. 769501-769502 will allow VoIP or NGN (Next Generation Network) trac from devices connected to the RJ11 or RJ45 interfaces, towards
the same internal VLAN.
Apart of the SIP and Megaco (H.248) self-conguration, it is also possible to make modications in the voice service congurations by updating
the Refs. 769501-769502 SW through download from the OLT via OMCI.
The Refs. 769501-769502 equipment has a DHCP client to get an IP address, alternatively the Refs. 769501-769502 could be congured with a
static IP. The conguration of the static IP or DHCP client is related to the WAN side and is enabled by the OLT.
2.12 WI-FI
2.12.1 Operational description
The Refs. 769501-769502 supports WI-FI, with an WI-FI interface currently operating in the 2.4GHz frequency.
The Refs. 769501-769502 complies with the following standards:
IEEE 802.11b (2.4GHz, 11 to 22 Mbps)
IEEE 802.11g (2.4Ghz, up 54 Mbps)
IEEE 802.11n (MIMO-OFDM 2.4GHz, 65Mbps to 300Mbps)
The ONT supports the following wireless security features:
WEP encryption (64/128 bits)
WPA (Wireless Protect Access) TKIP
WPA2 AES
Page 18
18
GPON ONT
WPA2 mixed
02.1x Authentication
Client access control through media access control (MAC) lter
Dynamic cryptography (TKIP and AES)
2.12.2 Block Diagram
The Refs. 769501-769502 circuit block diagram is presented in the gure bellow showing all oscillators in the device and its frequencies, Figure 9.
Intentional radiators in the circuit and radio signal path between circuit blocks are also shown.
SoC
GPON
MAC
ETH
MAC
DDR3
FMI
Flash
SCAP
O
E
CDR
CaTV
Type F
SLIC
2xFXS
SPI
RJ11
LED Driver
PCIe
PCIe
POWER
DC/DC
12V
VOICE
CTRL
CATV
AMP
390 KHz
25 MHz
20 MHz
700 KHz
100 MHz
125MHz
240 MHz
533 MHz
600 MHz
800 MHz
WIFI 2x2
2.4GHz
DDR3
RJ11
RJ45
RJ45
RJ45
RJ45
Figure 2-9: Refs. 769501-769502 circuit block diagram
Page 19
EN
19
2.12.3 Refs. 769501-769502 WI-FI Antennas
The ONT provides a MIMO 2x2 topology Wireless antenna capability.
The ONT has internal, Omni-directional antennas with a gain of 1.6dBi.
2.13 Multiple QoS per VLAN
The Refs. 769501-769502 supports 802.1p QoS per VLAN services in which several ows (one per allowed pbit) are embedded in the same VLAN.
According to the applied conguration, the Refs. 769501-769502 performs a per-ow QoS policy: dropping trac marked with not allowed pbits
and limiting to the congured value the data rate of the allowed ows.
The Refs. 769501-769502 performs transparent VLAN translation. It is transparent to upper layer protocols, such as ARP, RIP, DHCP, IGMP, PPP, etc.
2.14 Policing/Rate Limiting
2.14.1 Downstream QoS
The OLT system provides several QoS mechanisms, that can be targeted to the ow characterized by one or two VLAN according with the type of
service, or can be targeted to the packets priority, where each p-bit is mapped in one of eight queues of each port.
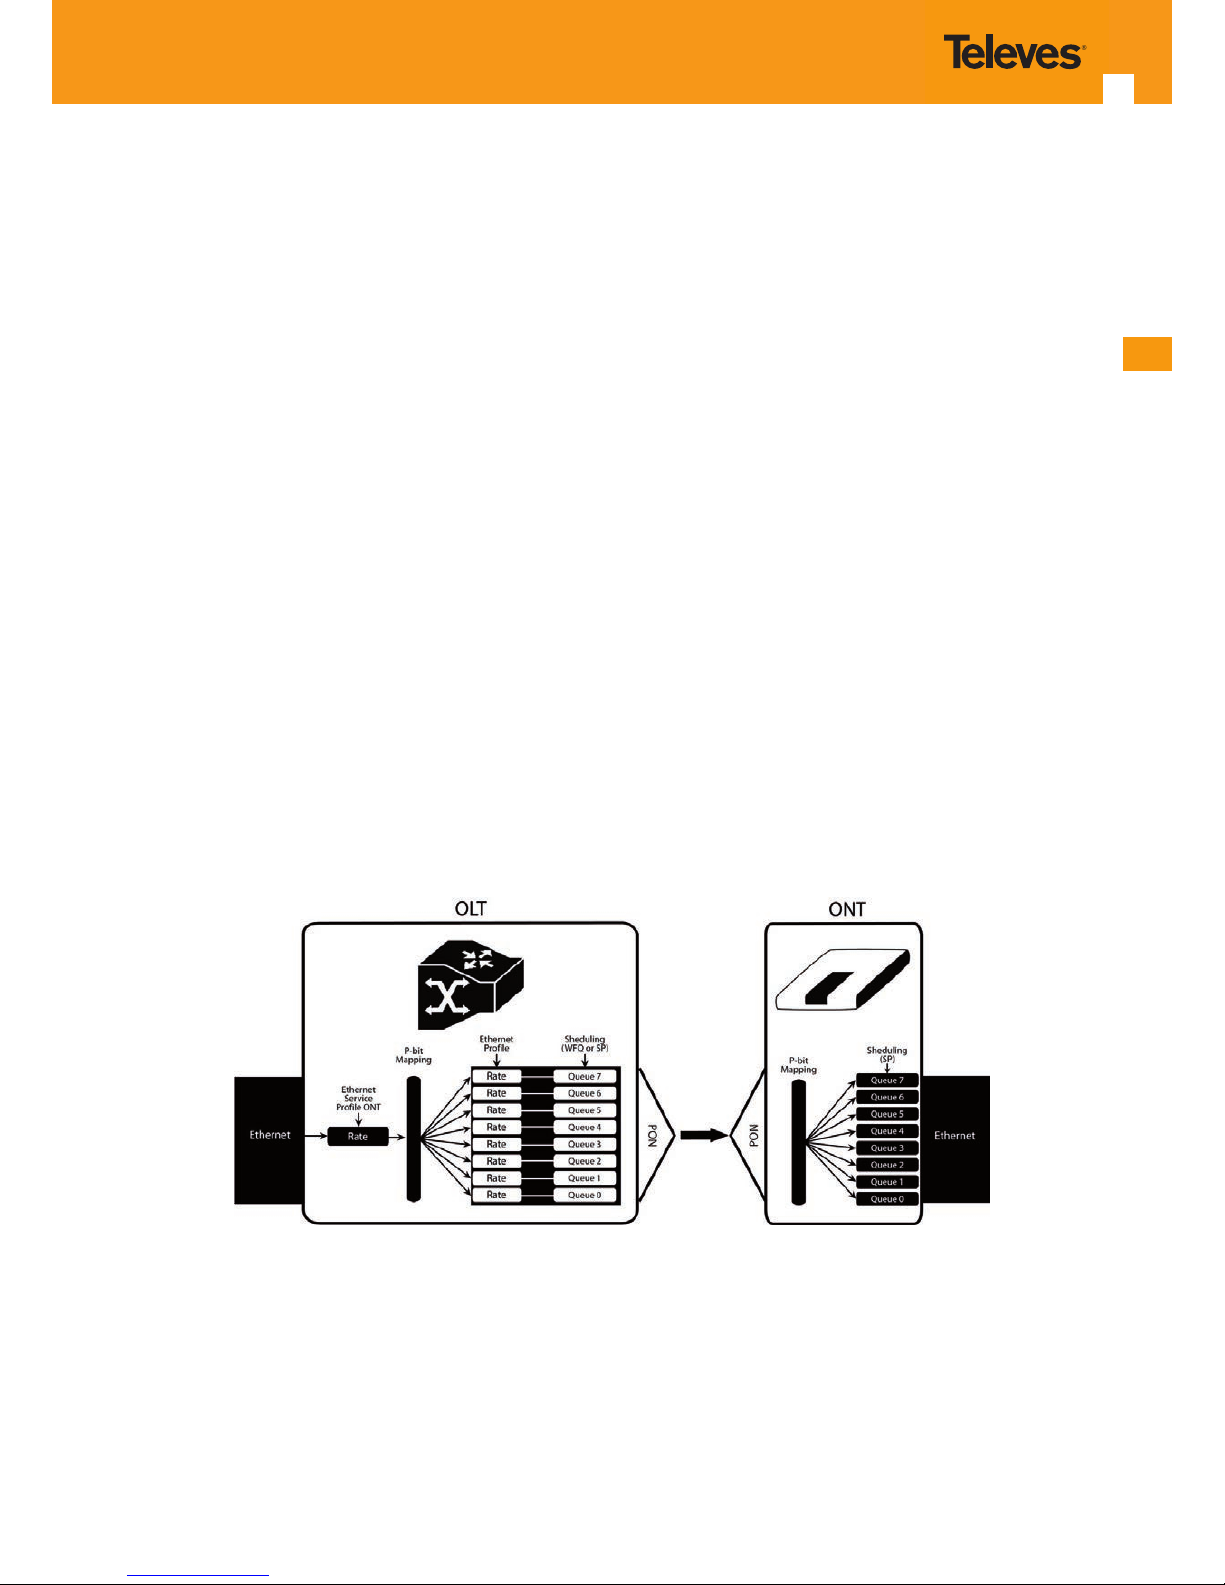
For each OLT ports are associated eight queues, for each of these queues is possible to congure the p-bit mapping in one of the queues, the
scheduler type (Strict Priority or Weighted Fair Queuing) and the minimum and maximum bandwidth of each queue.
In the downstream direction the ingress trac rst passes by a policer congured to each ONT service, which is dened by one or two tags. After
this the trac is put in a queue according with the p-bit/queue mapping. Each of these queues is associated with a scheduler and a policer. Then
the trac ows to the GPON interface and when it arrives to the ONT it will pass by a mapping block which will map the trac in one of the eight
queues according with the p-bits, these queues have a Strict Priority scheduler in order to guarantee that the most prioritized trac passes rst.
Figure 2-10: Downstream QoS Diagram
2.14.2 Upstream QoS
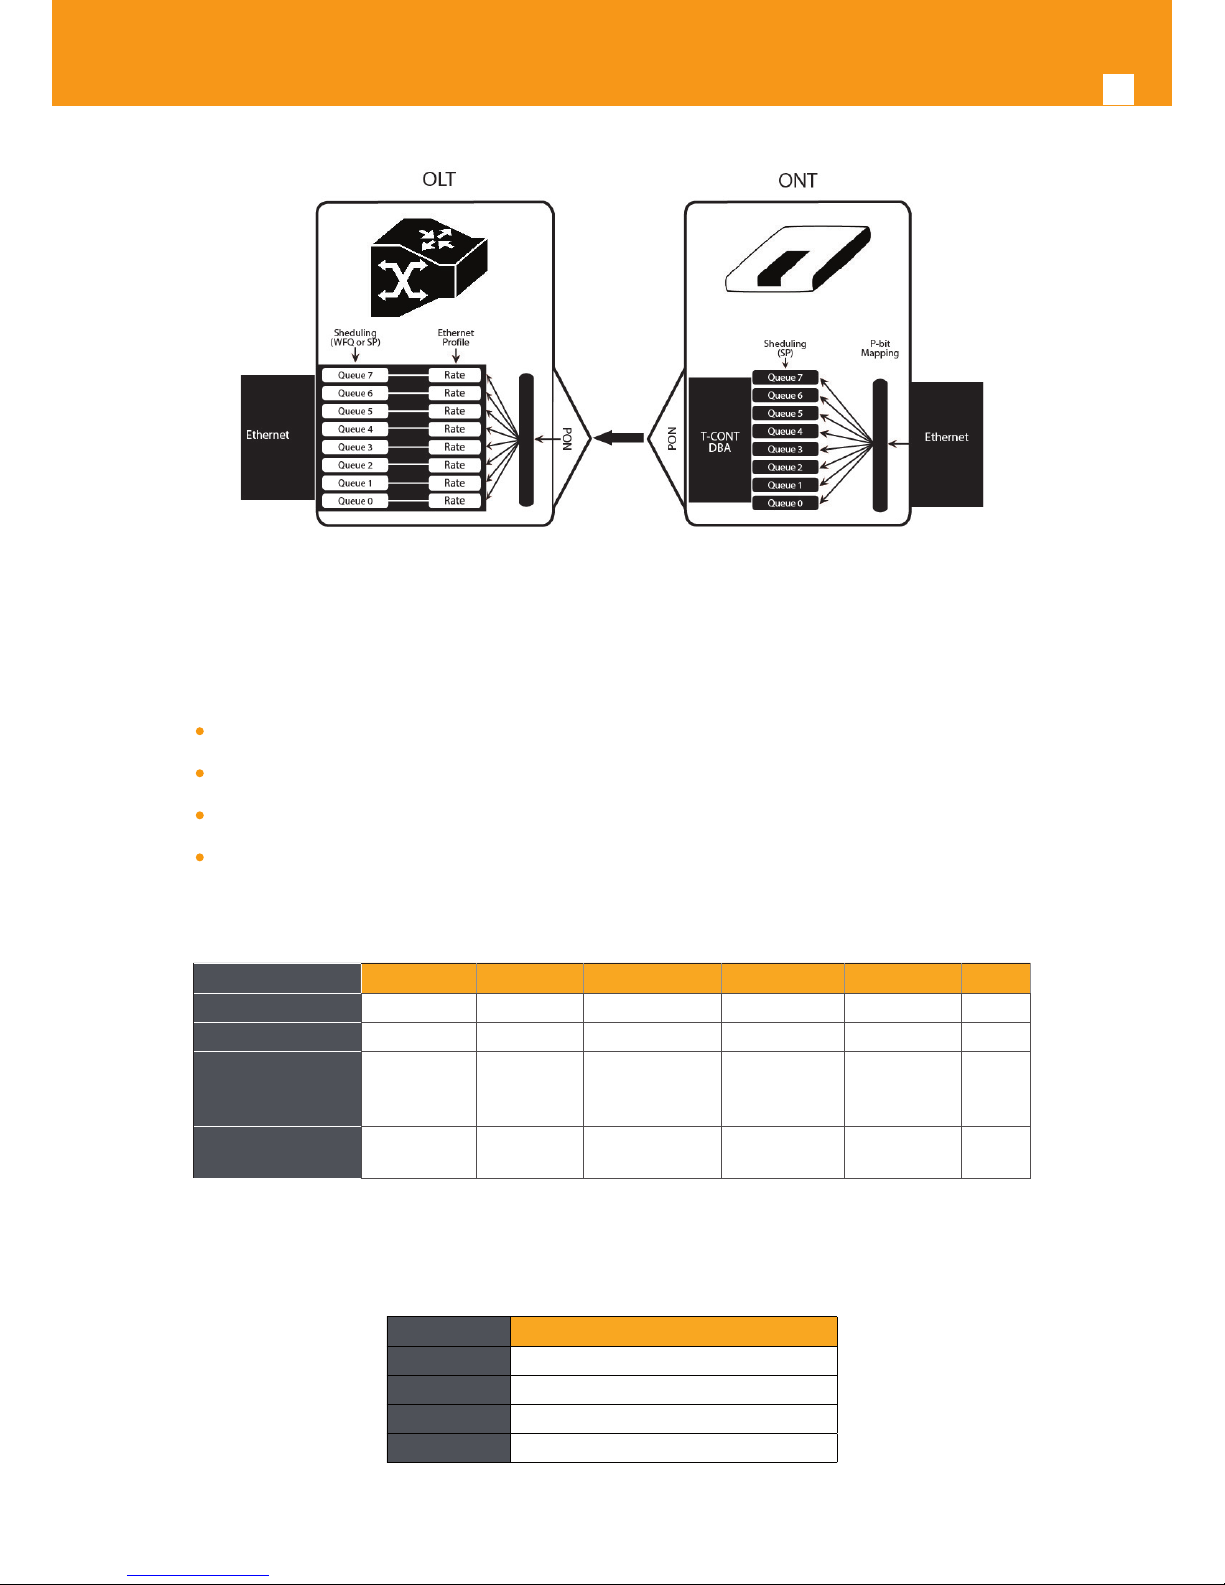
In the upstream direction, for each T-CONT the ingress trac in the ONT passes by a mapping block that maps the trac in one of the eight queues
according with the p-bit, these queues have a Strict Priority Scheduler. The ONT “waits” until the OLT assigns a transmission timeslot for that TCONT, so that the most prioritized queues are the ones that transmit rst. In the OLT ingress, the trac is put into a queue according with what
is dened in the queue/p-bit mapping. Each of these queues has an associated scheduler and policer that control the trac sent to the uplink.
Page 20
20
GPON ONT
Figure 2-11: Upstream QoS Diagram
2.14.3 Dynamic Bandwidth Allocation (DBA)
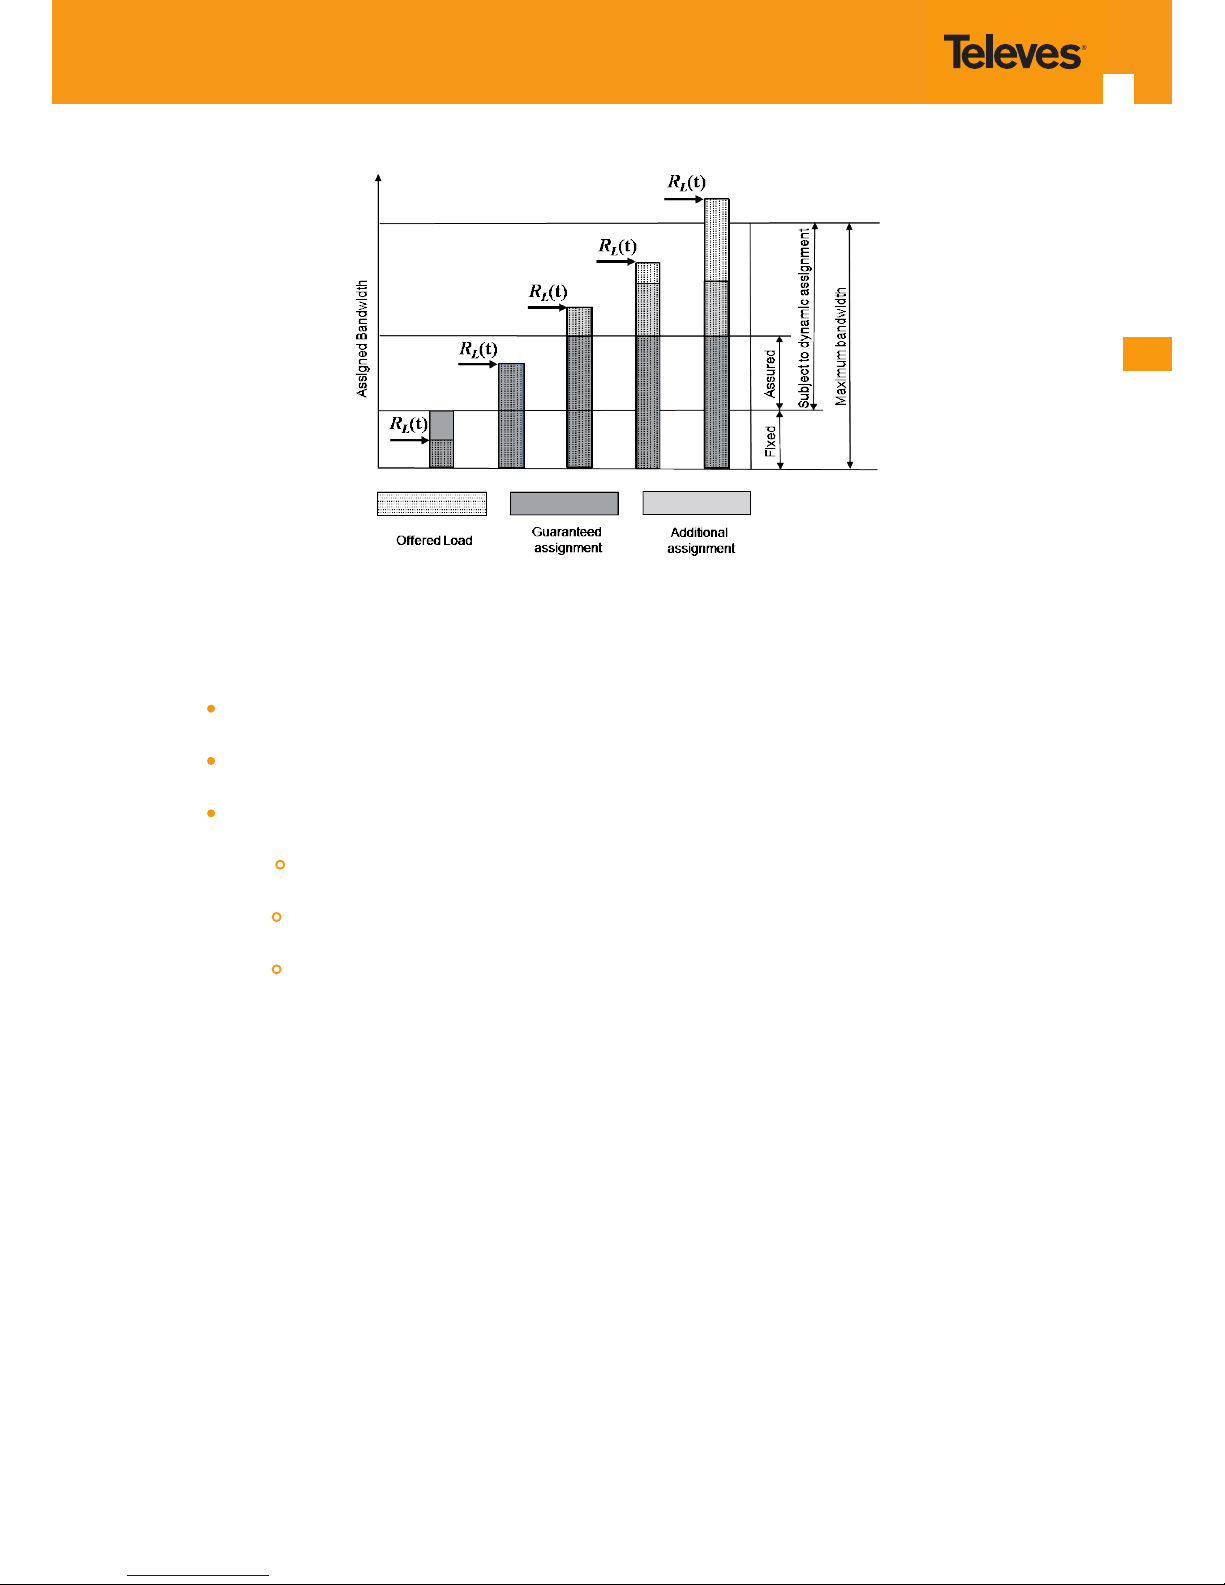
The DBA (Dynamic Bandwidth Allocation) is available in order to optimize the upstream bandwidth. This mechanism consists in dening an adequate T-CONT to the service trac in question. There are ve types of T-CONT, dened by the Fixed, Assured and Maximum Parameters:
Type 1: Only xed Bandwidth;
Type 2: Only Assured Bandwidth;
Type 3: Assured+Maximum Bandwidth;
Type 4: Only Maximum Bandwidth (Best Eort);
Type 5: Fixed+Assured+Maximum Band
T-CONT Type 1 Type 2 Type 3 Type 4 Type 5 Units
Fixed BW- R
F
R
F1
0 0 0 R
F5
[b/s]
Assured BW- RA 0 R
A2
R
A3
0 R
A5
[b/s]
Max Bw - RM RM1 = R
F1
RM2 = R
A2
R
M3
> R
A3
R
M4
RM5 >
RF5 + R
A5
[b/s]
Bandwidth Eligibility
0 0 Non-Assured
BW - R
NA
Best-Eort
- R
BE
RNA / R
BE
Table 2-1: T-CONT types denition
In each GPON interface there are 1024 Alloc-ID (T-CONT identiers) available, provided to manage ONT services. They are distributed in the following way:
Alloc-ID Allocation Type
0-127 Default Alloc-ID (Dynamic or Static)
128-255 Reserved
256-639 Dynamic or Static
640-1023 Static
Table 2-2: Alloc-ID’s distribution by T-CONT type
Page 21
EN
21
Figure 2-12: Trac distribution by service/client
2.14.4 Upstream QoS scenarios
8 priority queues
Strict-priority
Upstream Scheduling:
Strict Priority (currently supported)
Strict Priority + rate controller (currently supported)
Strict Priority + WFQ (can be SW supported)
Page 22
22
GPON ONT
3. General Specications
3.1 Interfaces
3.1.1 GPON
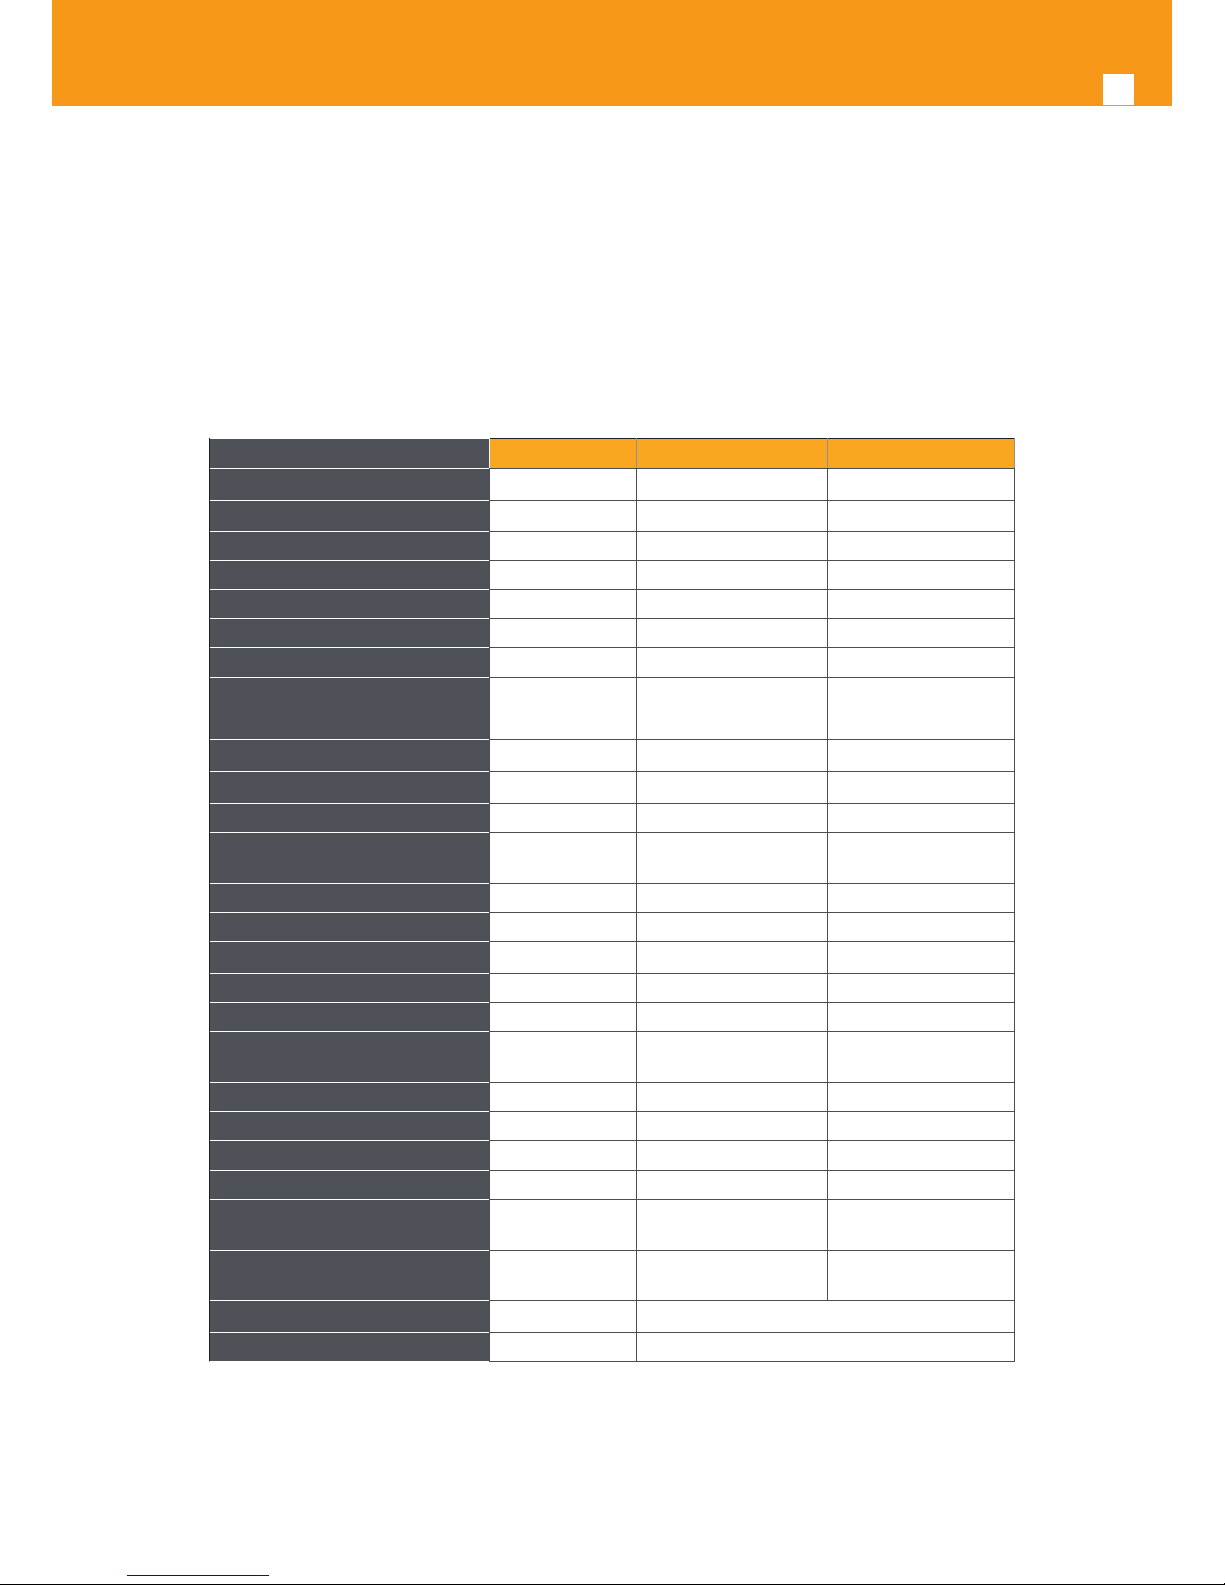
The Refs. 769501-769502 GPON G.984.x layer uses 1490nm downstream and 1310nm upstream optical wavelengths, with 2,488Gbps downstream
and 1,244Gbps upstream by using an SC/APC protected optical connector.
3.1.1.1 Optical interfaces
Items Unit B+ C+
ONT Tx ONT Tx
Nominal bit rate
Mbps
1244.16 1244.16
Operating wavelength
nm
1260-1360 1260-1360
Line code
--
Scrambled NRZ Scrambled NRZ
Minimum ORL of ODN
dB
>32 >32
Mean launched power MIN
dBm
+0.5 +0.5
Mean launched power MAX
dBm
+5 +5
Launched optical power without
input to the Tx
dBm
Less than Min
sensitivity -10
Less than Min
sensitivity -10
Maximum Tx Enable 16 16
Maximum Tx Disable 16 16
Extinction ratio
dB
>8.2 >8.2
Tolerance to the Tx incident light
power
dB
>-15 >-15
SLM Laser – MAX −20 dB width
nm
1 1
SLM Laser – MIN SMSR
dB
30 30
ONT Rx ONT Rx
Receiving bit rate
Mbps
2488.32 2488.32
Receiving wavelength
nm
1480-1500 1480-1500
Max reectance of equipment,
measured at Rx wavelength
dB
<-20 <-20
Bit error ratio
--
<-10
-10
<-10
-10
Minimum sensitivity
dBm
-27 -30*
Minimum overload
dBm
-8 -8*
Upstream optical penalty
dB
0.5 0.5
Consecutive identical digit immunity
bit
>72 >72
Tolerance to reected optical
power
dB
<10 <10
ONT Rx Video
Receiving wavelength
nm
1550-1560
Table 3-1: Optical interfaces specications
* ONT RX= -8~-30 dBm (The ONT7-RGW sensitivity assumes the use of the optional RS (255,239) FEC capability of the G-PON TC layer with the current
class B+ ONU detector technology; The ONU overload is set at –8 dBm to be common with the class B+ value, even though in this application –10 dBm is
sucient).
Page 23
EN
23
Optical solution: B+ and C+.
Connector type: SC/APC.
IEC 60825-1: “Class 1 Laser Product’’.
The B+ and C+ triplexer is embeeded on the ONT7-RGW equipment version.
ONU Single Fiber - G.984.2 (03/2003) + G.984.2 Amd 1 (02/2006) and 2 (03/2008), G.983.3 (03/2001).
Optical Metering – G.984.2 Amd 2 Table IV.1/G.984.2 – Optical Line Supervision related measurement specications (the accuracy of the measurement is
+/-3dBm maximum).
3.1.2 Ethernet
Ethernet is the wired LAN technology and is revised in the IEEE 802. 3 standard. At the OSI reference system, Ethernet is at the Data Link layer. In
the ONT7-RGW equipment the LAN type of physical interfaces is 10/100/1000BASE-T AUTO-MIX Ethernet type over RJ45 conectors.
3.1.3 RF Overlay
Broadcast video signal travels over ber from the CO in the 1550nm wavelength and is demuxed and converted in the Refs. 769501-769502 to a F
connector (75 Ohm) RF Overlay interface to deliver a RF TV signal going from 47MHz up to 1GHz of bndwidt.
Page 24
24
GPON ONT
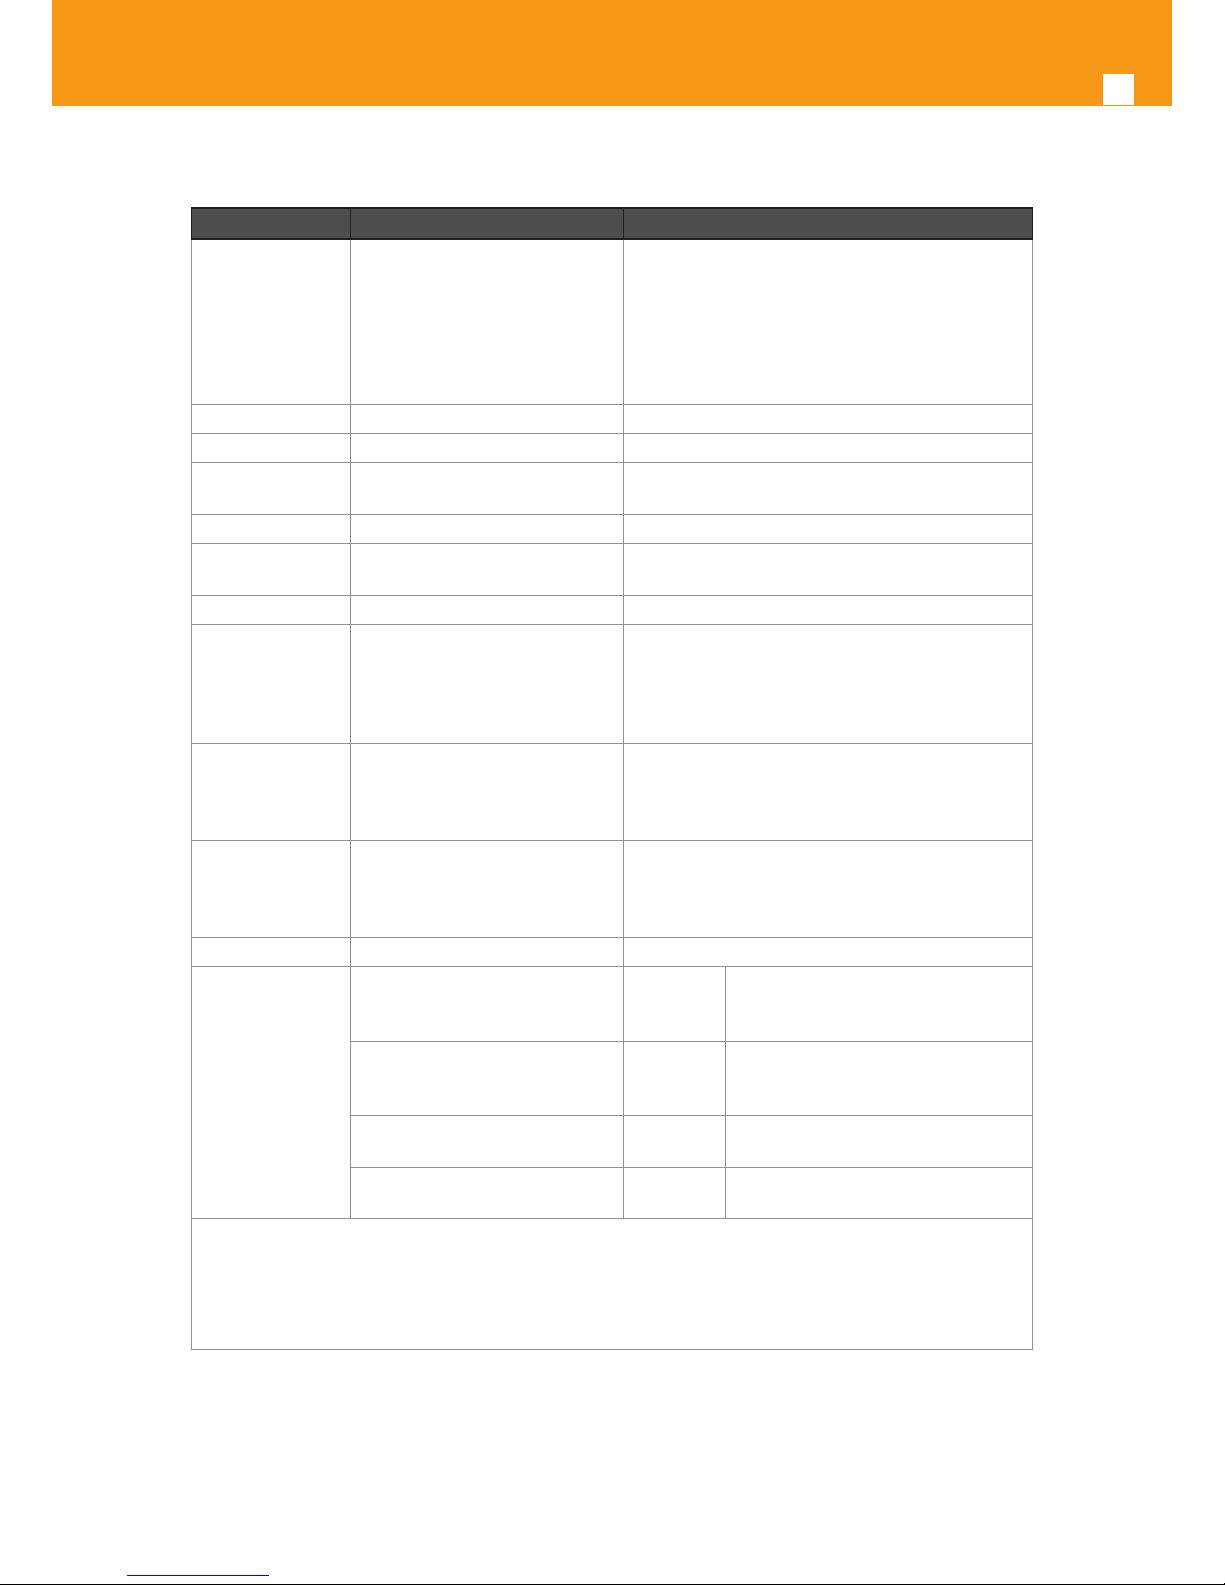
3.1.4 FXS
Items State Description
Pulse Dialling Pulse Frequency: 10 Hz (8 Hz to
12 Hz)
Pulse Relation: 66,6% (33% to
75%)
Interdigital Pause and Pre-Dialling: 400 ms (min)
-
DTMF - According to ETSI CTR 21 [1]
Clip - According to ETSI 300 659-1
Clip on Call Wait-
ing
- According to ETSI 300 659-2
DC voltage (V) -48V (-46 to -54) Loop Current
Characteristics (A)
20mA (min) to 60mA (max) -
Ifeed Max. (A) 45mA Impedance and
Transmition Requirements (Ω)
Q.552 [4] (11/96) of ITU-T
220Ω+820Ω//115nF.
A telephone that comply with transmission requirements dened in CTR 38, should comply
with SLR, RLR and STMR (4.2.2.1, 4.2.2.2 and 4.2.3)
standard requisites, when connected to a FXS
interface.
ILA (A) 20 – 45 mA 5 bit parameter which sets the current limit for
DC feed (DC feed and battery switch are programmed and calibrated to ILA=26mA, VOC=48V,
VAS=3V, bshv=5V).
Ringer voltage (V) DC oset: 48V
AC voltage: 75Vrms +/- 0.5%
Frequency: 25Hz +/- 3%
-
Ringing signal normal ringing 1 sec ring / 5 sec pause (interval = 6 sec).
Hook ash on-hook - register recall/hook
ash
100 msec Minimum time of recognition of “on-
hook” when hook-ash feature does
not exist
on-hook - register recall/hook
ash
1000 msec Minimum time “on-hook” recogni-
tion when hook-ash feature does
exist
o-hook 40 msec minimum time “o-hook” recogni-
tion
intervall 160msec -
400msec
Time calibrated break pulse duration
for register recall recognition
NOTE:
FXS interface specic parameter values vary according to country adopted standards. Refs. 769501769502 FXS interface specications table values are congurable at the web management interface at
the menu Voice, item SIP basic settings, by selecting the local(Country) where the Refs. 769501-769502
will be used. Please refer to section SIP BASIC SETTING, for details on this conguration.
Table 3-2: FXS interface specications
Page 25
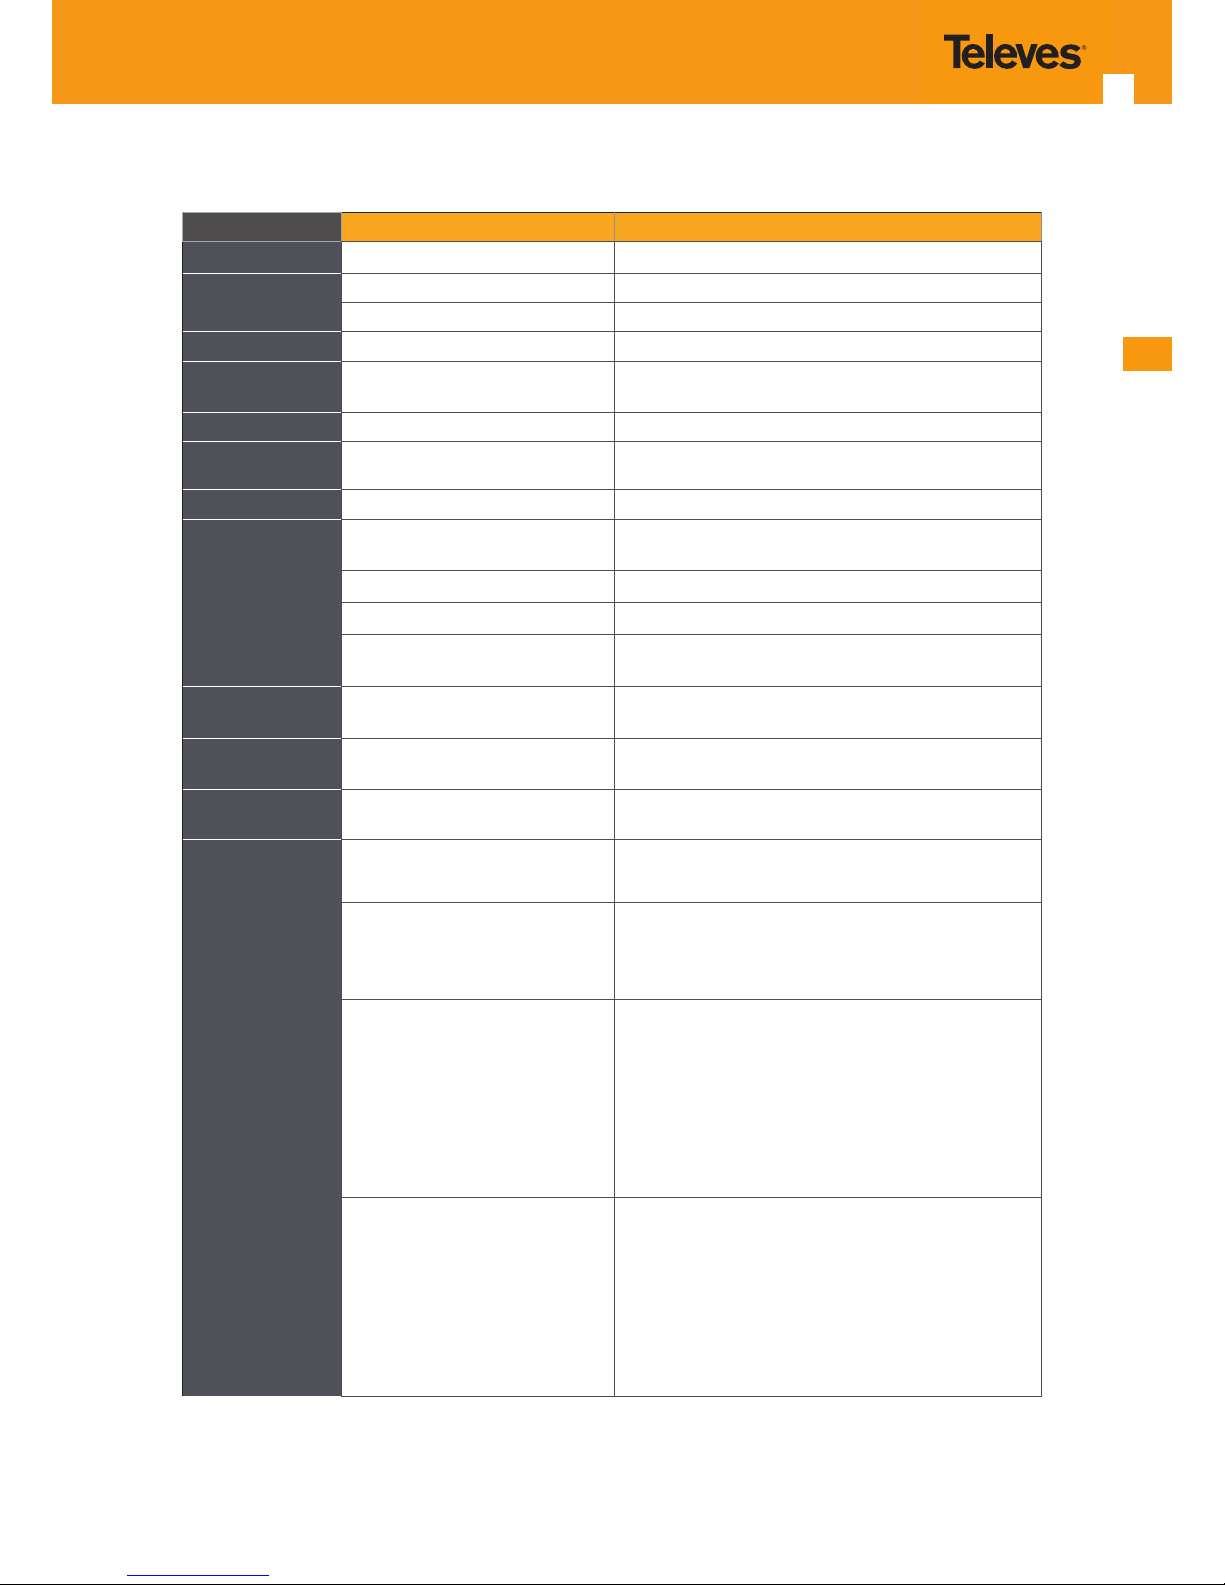
EN
25
3.1.5 WI-FI
Items Compliance Description
IEEE 802.11 b/g/n -
Bit Rates 802.11 b/g 1, 2, 5.5, 6, 9, 11, 12, 18, 24, 36, 48 and 54Mb/s
802.11 n Up to 300Mb/s over two spatial streams
SSID - Up to 8
Operation Fre-
quencies
- 2.4GHz (ISM) or 5GHz (U-NII)
Channels - 20MHz and 40MHz channels
MIMO - 2x2
MCS - supported values: 0-15 and 32
Wireless Security WEP 40bit secure key and 24 bit as dened in 802.11-
2007
WPA
WPA2
AES encryption/de-encryption coupled to TKIP (as de-
ned in 802.11-2007 and 802.1X)
Short Guard Interval
SGI support -
Space-Time Block
Coding
STBC support -
Transmit Power - Up to +18dBm
Receive Sensitivity
Mode b (8% PER) 1Mb/s: -96dBm
11Mb/s: -88dBm
Mode g (10% PER) 6Mb/s: -90dBm
12Mb/s: -89dBm
54Mb/s: -75dBm
Mode n/2.4GHz (10% PER) 1Mb/s: -96dBm
54Mb/s: -75dBm
M0/20MHz: -86 dBm
M0/40MHz: -83 dBm
M15/20MHz: -69 dBm
M15/40MHz: -69 dBm
Mode n/5GHz (10% PER) 6Mb/s: -89 dBm
54Mb/s: -74 dBm
M0/20MHz: -85 dBm
M0/40MHz: -82 dBm
M15/20MHz: -68 dBm
M15/40MHz: -68 dBm
Table 3-3: WI-FI specication
Page 26
26
GPON ONT
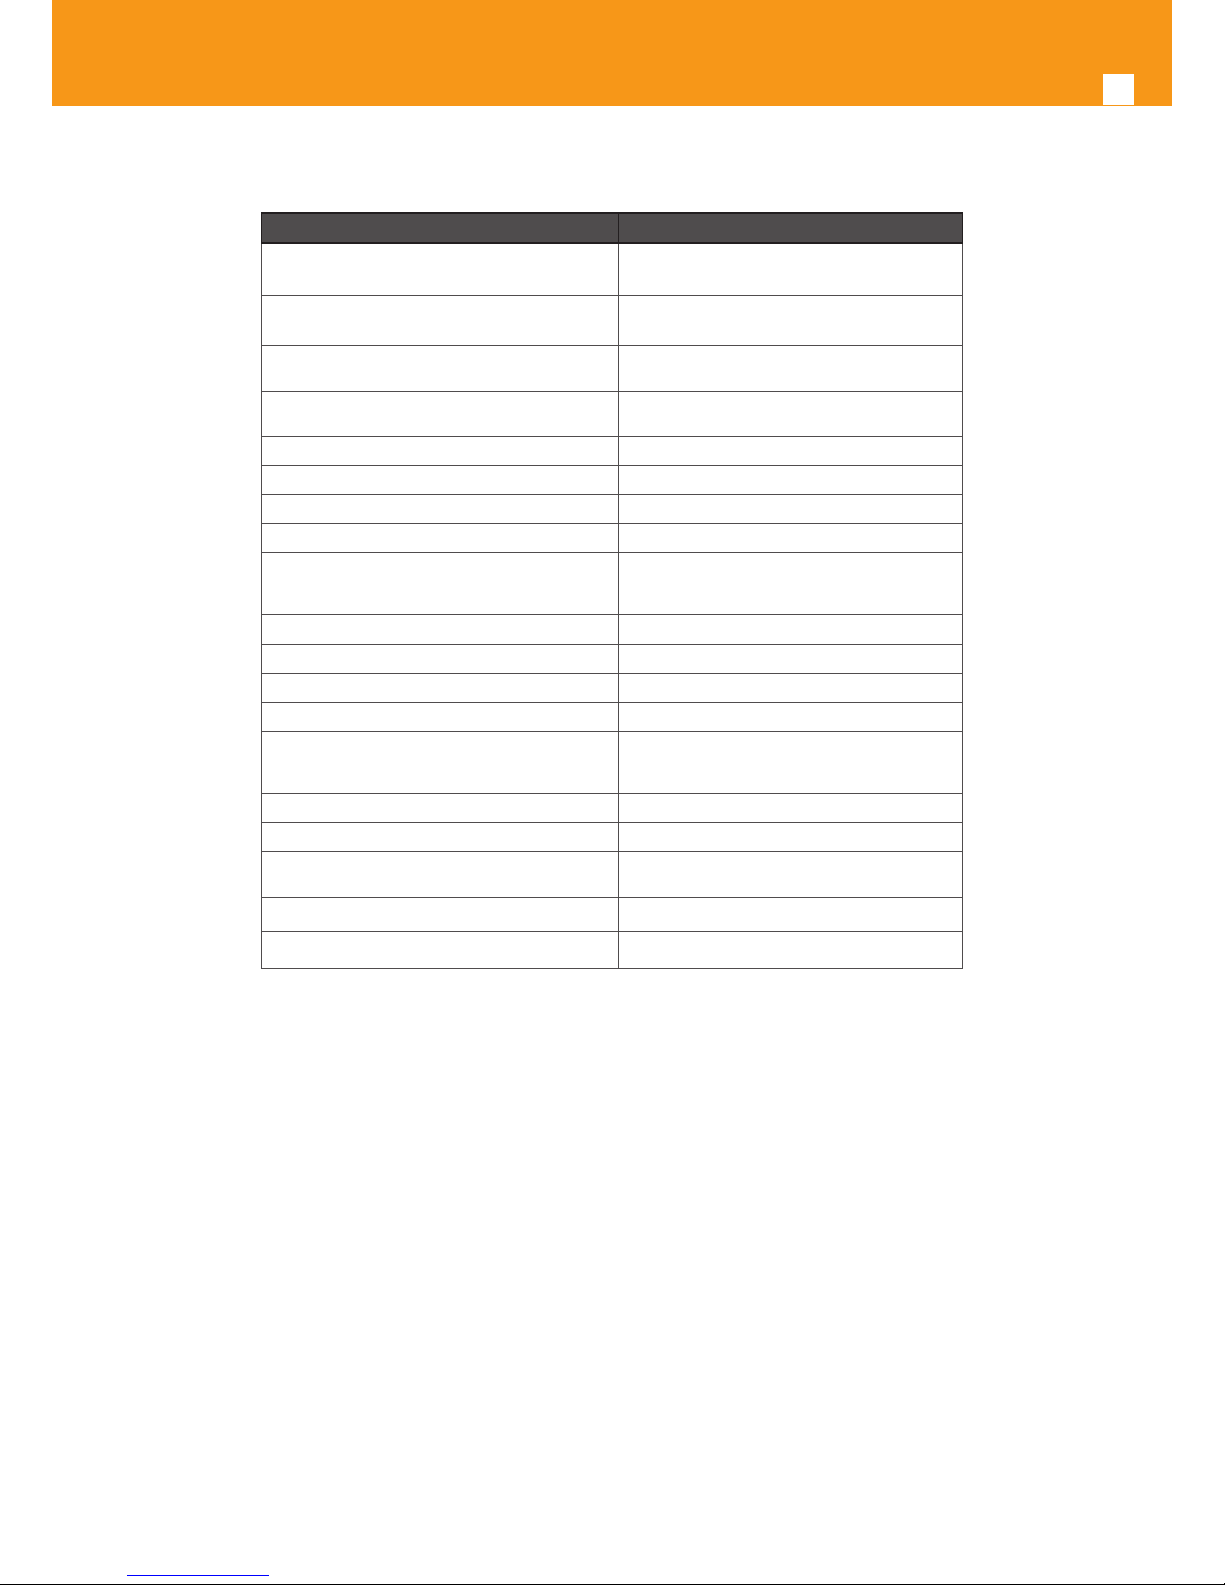
3.2 General Features
Features Refs. 769501-769502
GPON
1x Singlemode Optical Fiber Cable
(SC/APC Connector)
Ethernet 10/100/1000Base-T 4x Ethernet UTP CAT5E direct or crossover
AUTO-MDIX cable (RJ45)
RF Video Overlay
(1)
1x Coaxial F type connector (75 Ohm)
FXS Ports 2x voice / fax RJ11 connector
USB Ports 2x USB 2.0
WI-FI (802.11b/g/n) Yes
ON/OFF button Yes
RESET button Yes
OLT Interoperability
(BBF.247)
Yes
DHCP Client Yes
Number of GEM ports 256
Number of T-CONT 32
Primary Power Connection (VDC) 12 (± 15%)
Primary Power Connection (VAC)
230V AC 50Hz ±2Hz
110V AC 60Hz ±2Hz
Power Supply (W)
(2)
19
MTBF (h) 404660
Size (mm) 210x210x40
Temperature (⁰C) -5 to 45
Humidity (%) 0 to 95
Table 3-4: General Features
NOTES:
(1) Optional ; Dependent on the Refs. 769501-769502 specic model
(2) An LPS power source is used to power the ONT equipment:
US/Canada:
The ONT must be powered by an external Listed Limited Power Source (LPS) or Class 2 Power source. The external power adapter must be LPS certied.
Rest of the World:
The ONT must be powered by an External CB approved Limited Power Source (LPS).
Page 27
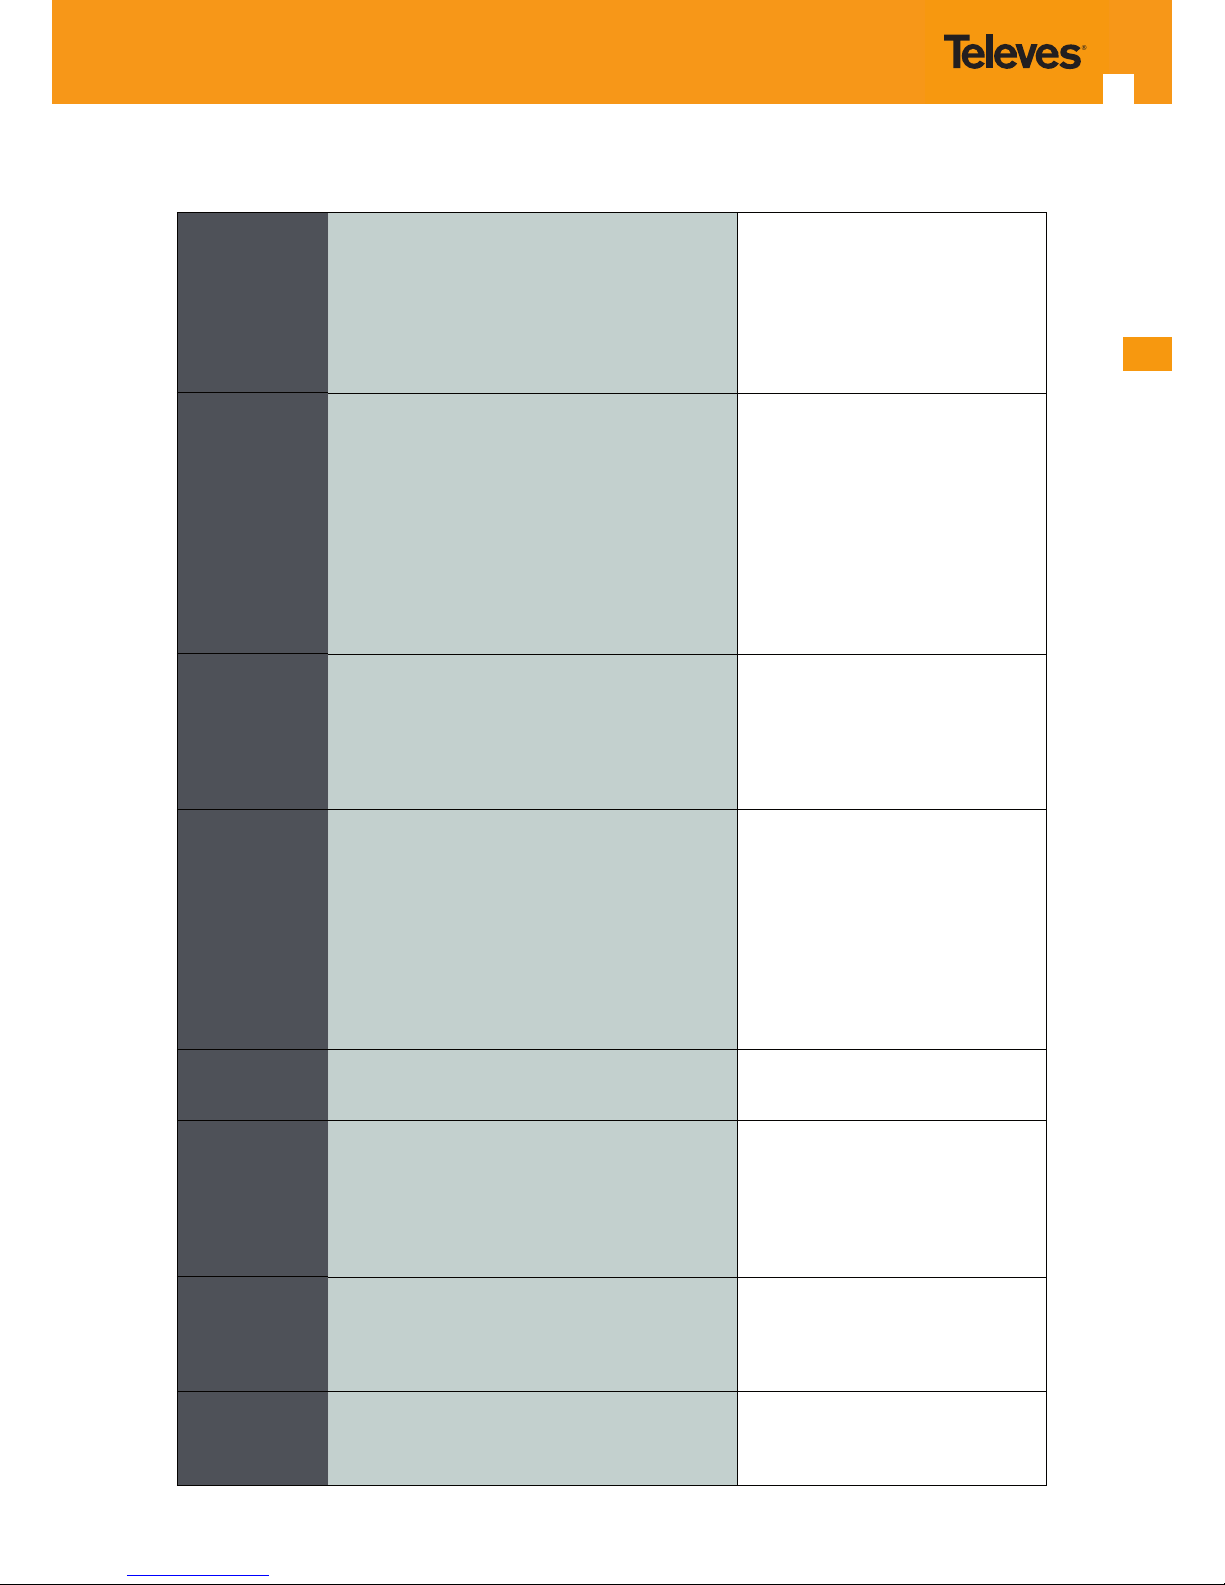
EN
27
3.3 General Service Description
GPON layer per
G984.x
> Comply with GPON standard: ITU-T G984.1/
G984.2/G984.3/G984.4;
> GPON Encapsulation Method (GEM) supports
Ethernet;
> Congurable AES Downstream and FEC Downstream and Upstream;
> Bitrates: 2488 Gbps (downstream) / 1244 Gbps
(upstream).
> Class B+ optics (28 dB);
> T-CONT:32;
> GEM-Port-IDs: 32.
L2/L3 layer > VLAN-ID to GEM port-ID mapping (per WT-156):
N:1 VLAN; 1:1;
> Transparent VLAN;
> Classication: IDSCP/TOS, 802.1p TCI, VLAN ID,
MAC address;
> Trac Management: up to 8 queues per T-CONT
in Priority-controlled mode or up to 16 queues per
T-CONT in Rate-controlled scheduling mode.
> 802.1q VLAN processing: Q-in-Q,
tagging, removing tag, replacing tag
or transparent forwarding;
> Routing: Network Access Translation
(NAT) and Network Access Port Translation (NAPT);
> Firewall;
> VPN;
> DHCP Client and Server;
> PPPoE Client;
> Performance: 1000 Mbps Bidirectional.
IPTV > IGMP v1/v2/v3 snooping;
> IGMP processing per VLAN ID to support group
of channels;
> Interactive services (Video On Demand);
> IPTV streams forwarding simultaneous: 128;
> IPTV prioritization using Quality of Service (QoS)
using 802.1p.
-
VoIP > T.38 Fax Relay;
> Fax/Data Bypass;
> Echo Canceller;
> Echo Canceller Length;
> Jitter Buer;
> Caller ID Generation;
> G.711 PLC;
> G.711 VAD and CNG;
> G.723.1;
> G.726 ADPCM;
> G.729 Annex A.
> G.729 Annex B;
> Caller ID and Call waiting;
> RTP/RTCP packet encapsulation;
> RFC 2833 support;
> In-band Signaling Detection and
Generation (dial, busy, ring-back, stutter, distinctive ring);
> 3-Way Conferencing;
> RFC 3261 support (SIP).
Ethernet > RJ-45 10/100/1000BASE-T;
> Support Auto-negotiation;
> Support auto MDI/MDIX.
-
Video Overlay > One port on a F Connector;
> 75 Ohm impedance (nominal).
> TV overlay: 1550nm -8dBm < Pin <
+2dBm;
> Analog bandwidth: minimum 47
MHz and maximum 1000 MHz;
> Channel number depends on PAL
B/G, PAL M, etc, systems.
WI-FI > IEEE 802.11 b/g/n > 802.11 b/g: 1, 2, 5.5, 6, 9, 11, 12, 18,
24, 36, 48 and 54Mb/s;
> 802.11 n: Up to 300Mb/s over 2 spatial streams.
Management > Web-based with GUI;
> Remote management over the OMCI, PLOAM,
OAM and TR-069, TR-104, TR-111, TR-142.
> Secure software download upgrade
via OMCI or TR-069;
> Embedded Telnet server for remote
management.
Table 3-5: Services
Page 28
28
GPON ONT
3.4 Optical metering
The equipment measures the downstream received power from the OLT in 1490nm and reports this value through OMCI. The accuracy of the
measurement is +/- 3dBm, maximum. Optionally, Refs. 769501-769502 has also the chance to have an embeded optical reective component
in order to increase the FTTH probing capabilities in a 50 centimeters resolution factor, which turns to have a single probing system to probe all
GPON network ONTs even when its number increases over Million customers.
3.5 Wavelength ltering
The optical interface has WDM lters that allow GPON coexistence with RF video services (1550-1560nm) and the new generation of NGPON1
technology, according to G.984.5 Recommendation.
ITU-T Rec. G987.1 is also granted for XGPON, (following FSAN NG-PON2).
In order to face the nal user´s demands, current GPON networks have to confront the rst evolution in terms of terminal equipments and actual
infrastructure. Migration will be available through a new wavelength planning, by allowing the co-existence of two dierent technologies over
the same ber. The ITU-T Rec. G987.1 provides a mechanism for GPON to XGPON migration with the possibility to achieve 2.5Gbps upstream path.
Nominally downstream will be 10 Gbps.
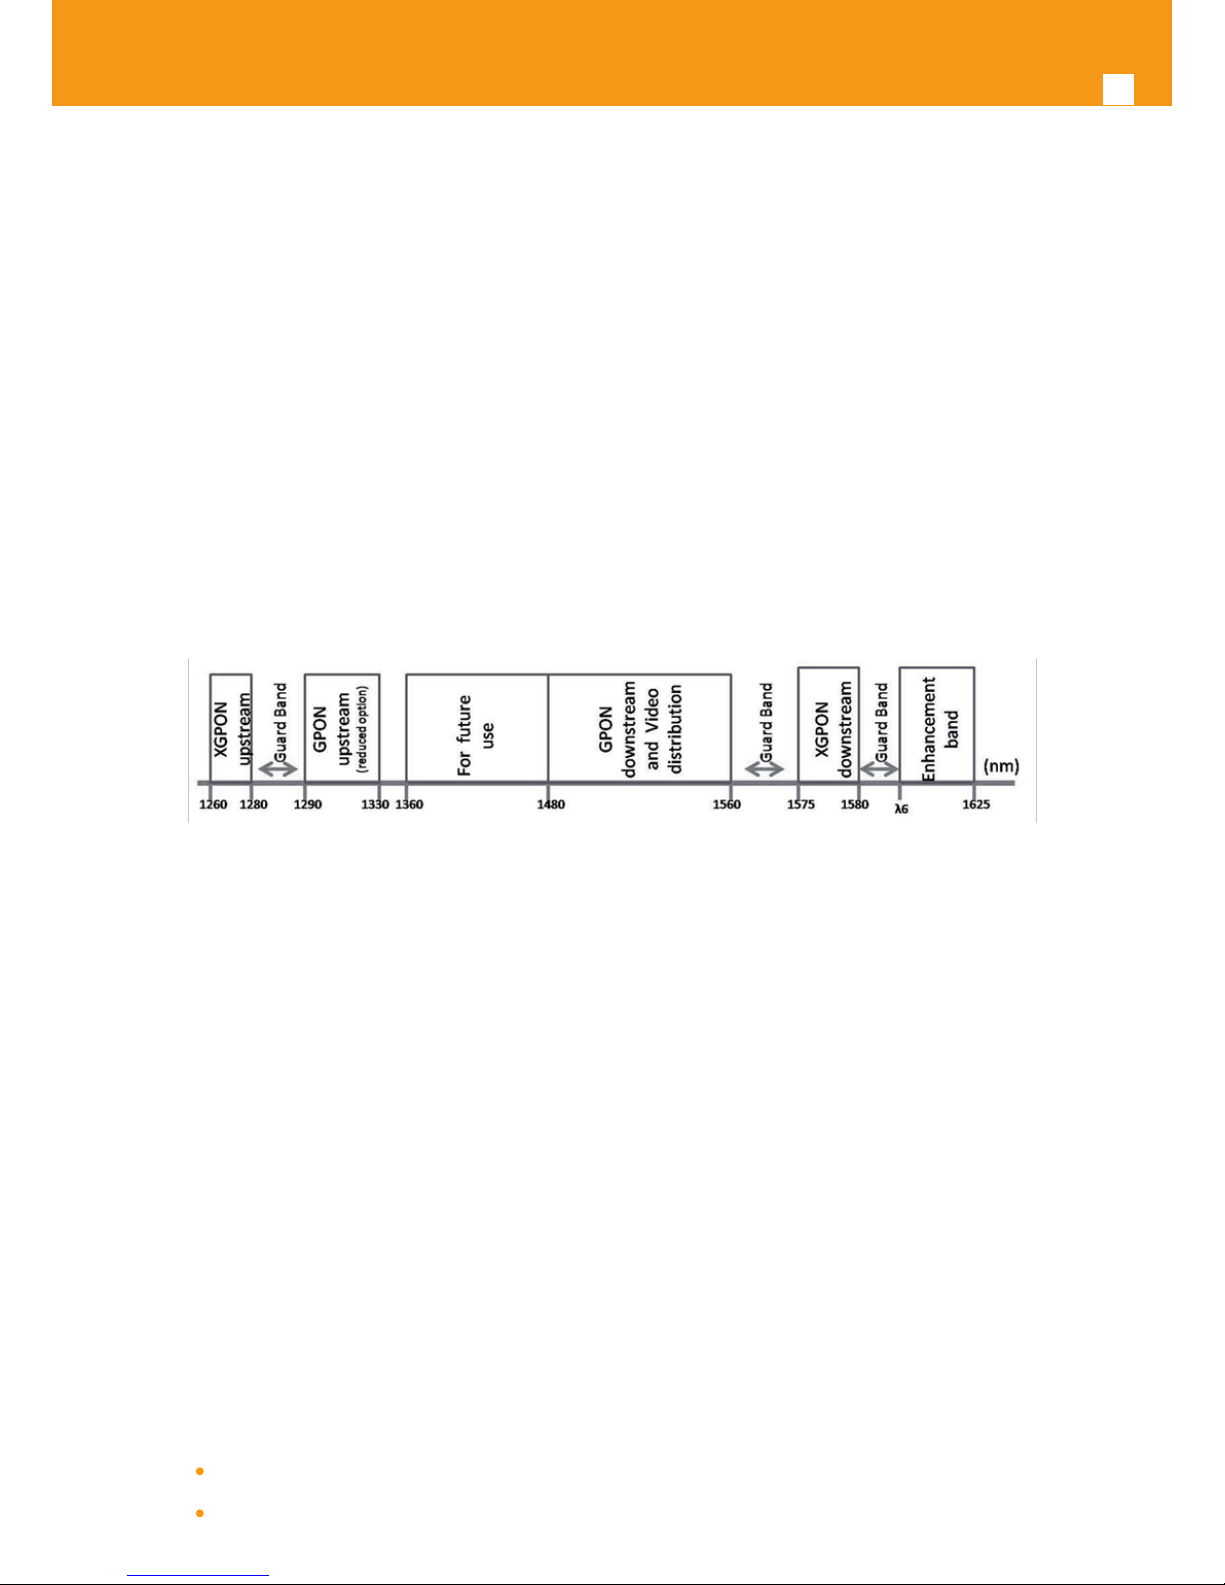
The next gure depicts the wavelength planning of ITU-T Rec. G987.1:
Figure 3-1: Wavelength planning
In order to accomplish to that plan, the upstream wavelength for GPON must be restricted to ONU (ONT) equipment based on the ordinary DFB
lasers, while the XGPON downstream signal range is dened from 1575 nm to 1580 nm and the XGPON upstream signal from 1260 nm to 1280
nm. For the coexistence of XGPON and GPON over the same ber, the CO requires a WDM lter that combines the downstream signal (1490 nm,
1555 nm and 1577 nm), isolating the 1310 nm and 1270 nm upstream signal, with the video signal. Also the wavelength of 1650 nm, used for ber
monitoring, has to be handled.
In addition, ONT devices require the use of a triplexer type transceiver that include an integrated lter or a discrete WDM lter to distinguish the
dierent signals that may be present on the ber. The current networks, equipped with ONT in accordance with the current ITU-T Rec. G984.5, will
be easily updated to XGPON.
Class B+ optical budget are the nominal requirement for coexistence of GPON and XGPON over the same optical ber. Taking this requirement
into account, the ber network architecture will not limit the future of the service provider business since GPON architectures, respecting B+ class
of the GPON, are easily updated by placing newest terminal equipments, namely XOLT and XONT, and by replacing the current WDM lter by the
new one in order to handle the new XGPON signals.
XGPON must support/emulate all GPON legacy services in case of total migration.
Like GPON, XGPON is required to support triple play services (data, voice and video), as well as mobile backhauling (accurate frequency/phase/
time synchronization) application through its high quality of service and high bit rate feature capabilities. Access to Ethernet services such as
point-to-point, multipoint-to-multipoint and rooted-multipoint Ethernet Virtual Connection services should be provided. Finally, as a global requirement, XG-PON needs to support IPv6.
3.6 GPON/Ethernet characteristics
GPON/Ethernet characteristics supported, both functional level and GTC-OMCI conguration, corresponds with the general mandatory characteristics dened in ITU-T G.984.3, G.984.4 and G.988 Recommendation:
PON interface: downstream operating rate 2.488 Gbits/s, upstream operating rate 1.244 Gbits/s;
32 T-CONT and 256 simultaneous GEM ports;
Page 29
EN
29
1:64 SR is granted once optical power transmission from the OLT side is up from -27/30dBm;
Unmarked or marked bandwidth management;
Upstream and downstream FEC;
Downstream AES encryption;
Ethernet ow control in client´s port: 802.3x and 802.3ab;
Ability to classify and modify VLAN labels (single or double labeling);
Ability to support multiple VLAN tags per service (Internet, IPTV, VoIP, ACS, etc) from Residencial Gateway. And ability to translate
those VLAN to one specic service VLAN on OLT side, like, IPTV service VLAN, Internet Service VLAN (SVLAN and CVLAN), and VoIP
Service VLAN;
802.1 DSCP for CoS support;
IEEE 802.1Q and 802.1p support;
Multicast snooping support IGMPv2 and IGMPv3;
Firmware upgrade through the PON interface following the mechanisms specied in the ITU-T G.984.4 and G.988, including a safe
dual rmware updates image system and the ability of back-up, allowing the SINGLE PORT Refs. 769501-769502 start in case the
software download fails, to enable a new software update.
3.7 GPON management
The system supports the conguration according to the recommendations described in ITU-T, G.984, G.988 and BBF TR-156.
Specically the next functionalities are obtained via OMCI for diagnostic (counters and alarms):
Refs. 769501-769502 conguration checking of the services provisioned;
Acquisition of the physical parameters of the SINGLE PORT GPON Refs. 769501-769502 interface;
Trac counters, statistics, errors, GPON interface status: by VLAN, by trac type, by priority;
Trac counters, statistics, errors, GbE interface status are only available by port;
Conguration parameters of services provisioned in the Refs. 769501-769502: T-CONT, GEMPORT, VLAN and GPON MAC tables;
Alarms/events included in the standards mentioned above.
•
•
•
•
•
•
•
•
•
•
Page 30
30
GPON ONT
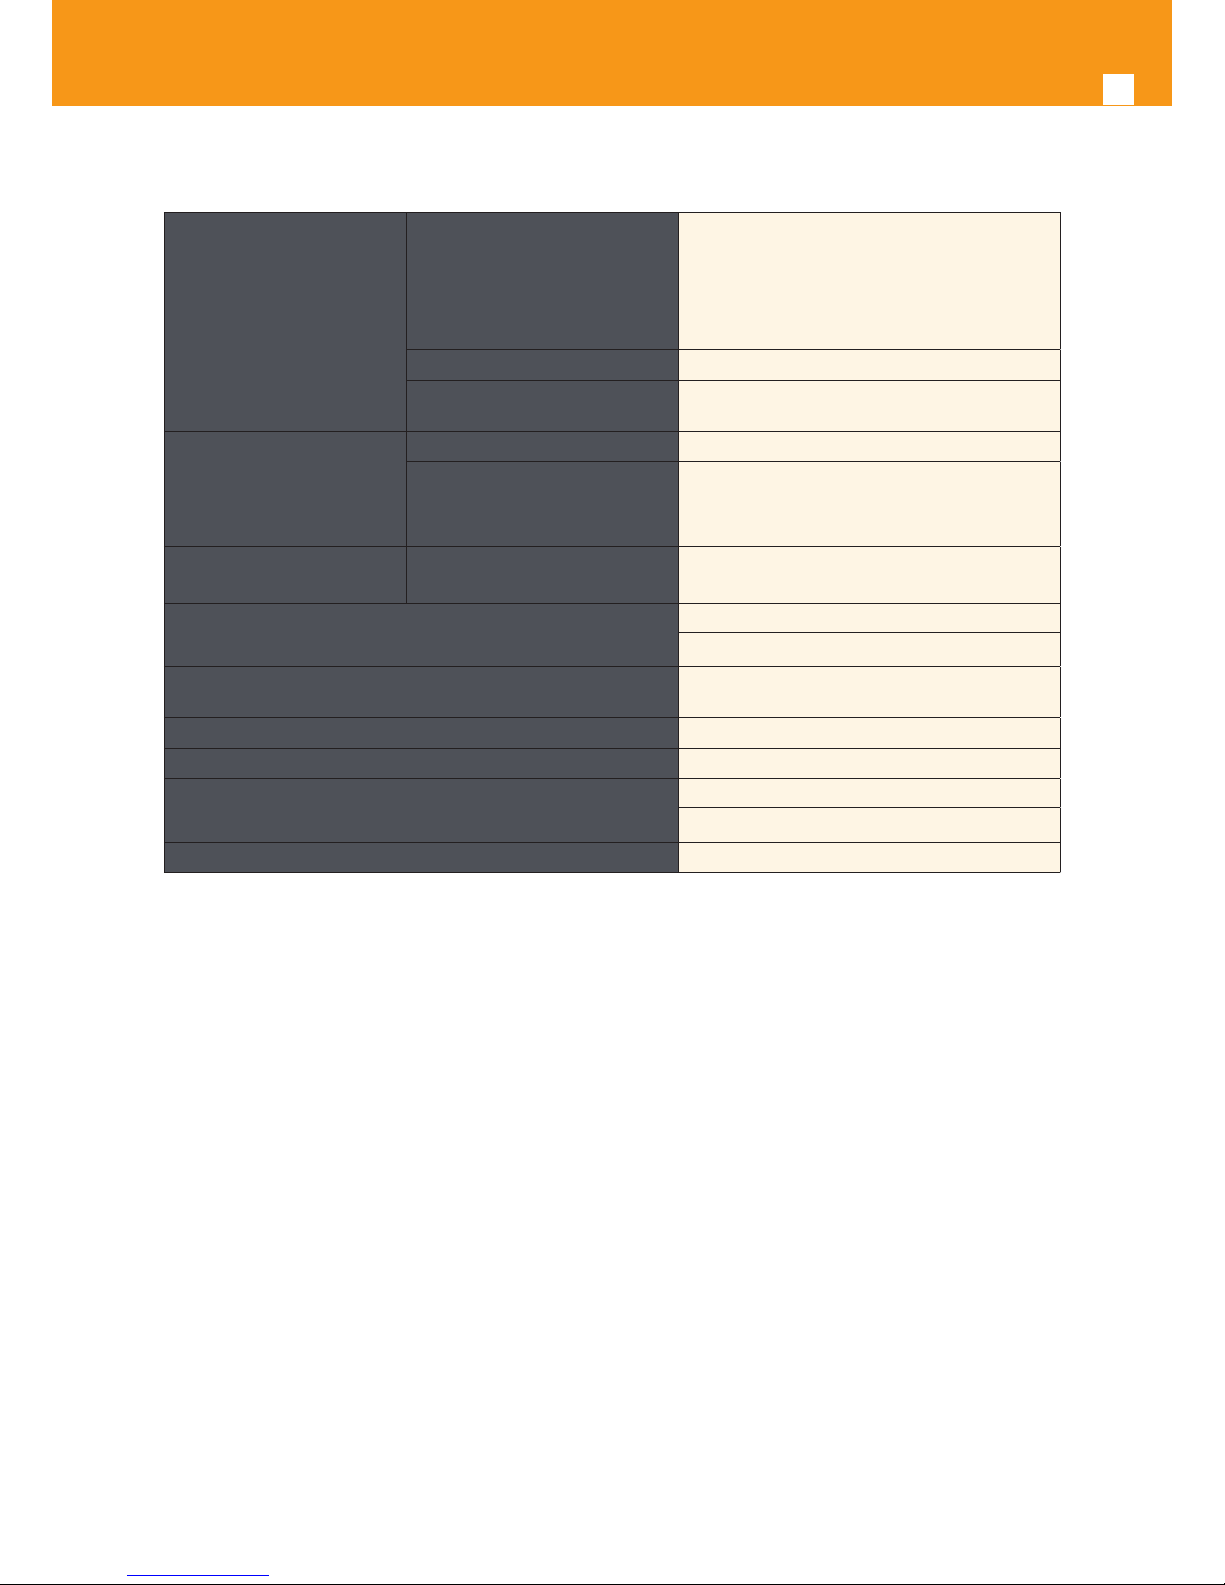
3.8 Standards
EMC
Standards
EMC Directive 89/336/EEC, EMC Addendum
Directive
92/31/EEC, EMC Addemdum Directive 91/263/
EEC
(Telecommunications Terminal Equipment
Directive)
Emissions EN50081-1, EN55022
Immunity
EN50082-1, EN61000-4-2, EN61000-4-3,
EN61000-4-4
Operating Limits
Temperature EN300019
Relative humidity, maximum EN300019
Environmental Standards Acoustic noise ISO 3743 (<45dBa)
Power and Grounding
ETSI EN 300 132-2 V2.1.1 (2003-01)
ETSI ETS 300 253: January 1995
Energy Consumption
European Code of Conduct on Energy Con-
sumption of Broadband Equipment V3
Safety and Protection EN/IEC 60950-1
Mechanical Resistance EN300019
Quality
RoHS 2002/95/EC Directive Compliance
CE - Conformité Européenne
Certication BBF.247 G-PON
Table 3-6: Standards compliance
Page 31
EN
31
4. Setup
4.1 Before installing Refs. 769501-769502 device
Check for site’s environmental conditions and look for power and optical access points nearby;
Do not install the device in environments where the temperature or humidity exceeds the standard limits;
This device is a passive cooling device. There are thermal holes in the surface of the box. To prevent the overheating do not
obstruct these thermal holes;
The Refs. 769501-769502 device is not designed for outdoor setup. Please place it in a convenient indoor/cabinet environment;
Use only the provided power kit. The use of a third party power adapter may not guarantee its proper operation;
To avoid any hazard or damage in your eyes, please never look directly into a bre optic connector;
Never assume that the laser beam is inactive or that the optical bre is switched o.
4.2 Connections
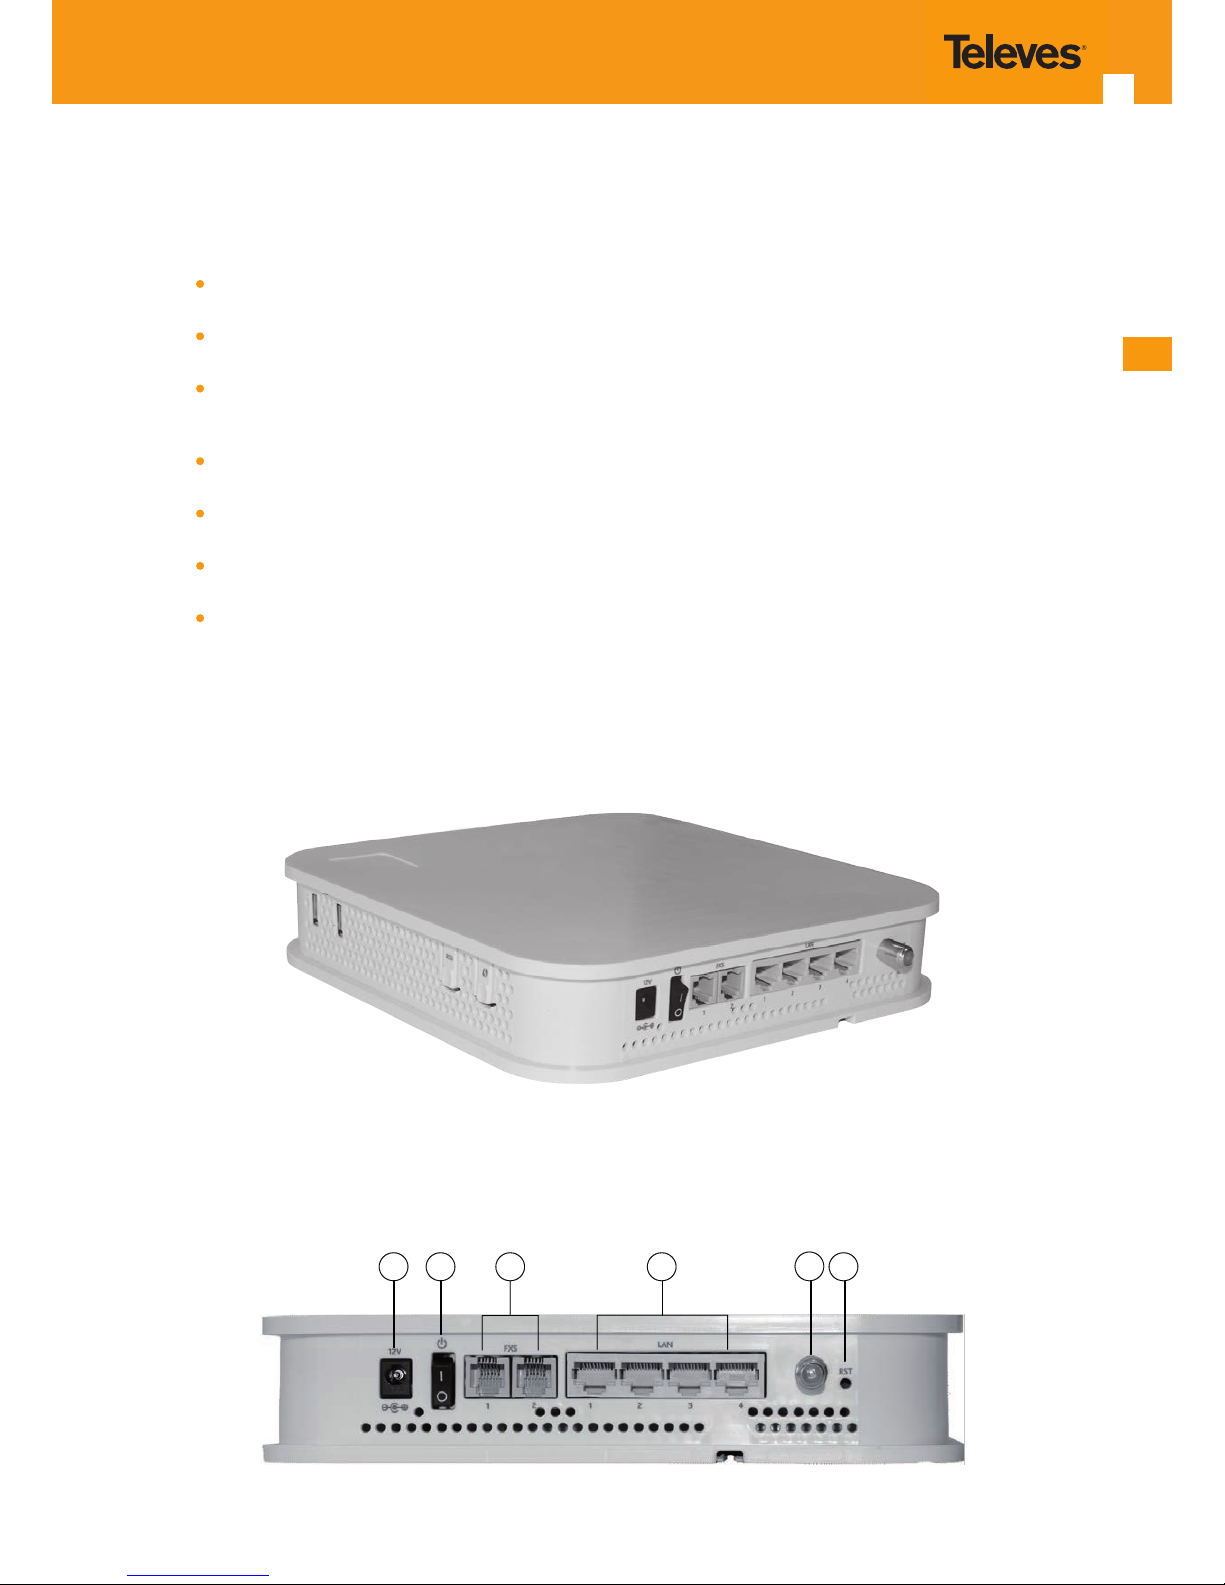
Refs. 769501-769502 connections are distributed by two side faces of the device Refs. 769501-769502 connections’ general view is show in the
following picture, Figure 4-1.
Figure 4-1: Refs. 769501-769502 connections general view
1 2 3 4 6
5
Figure 4-2: Refs. 769501-769502 connections 1
Page 32
32
GPON ONT
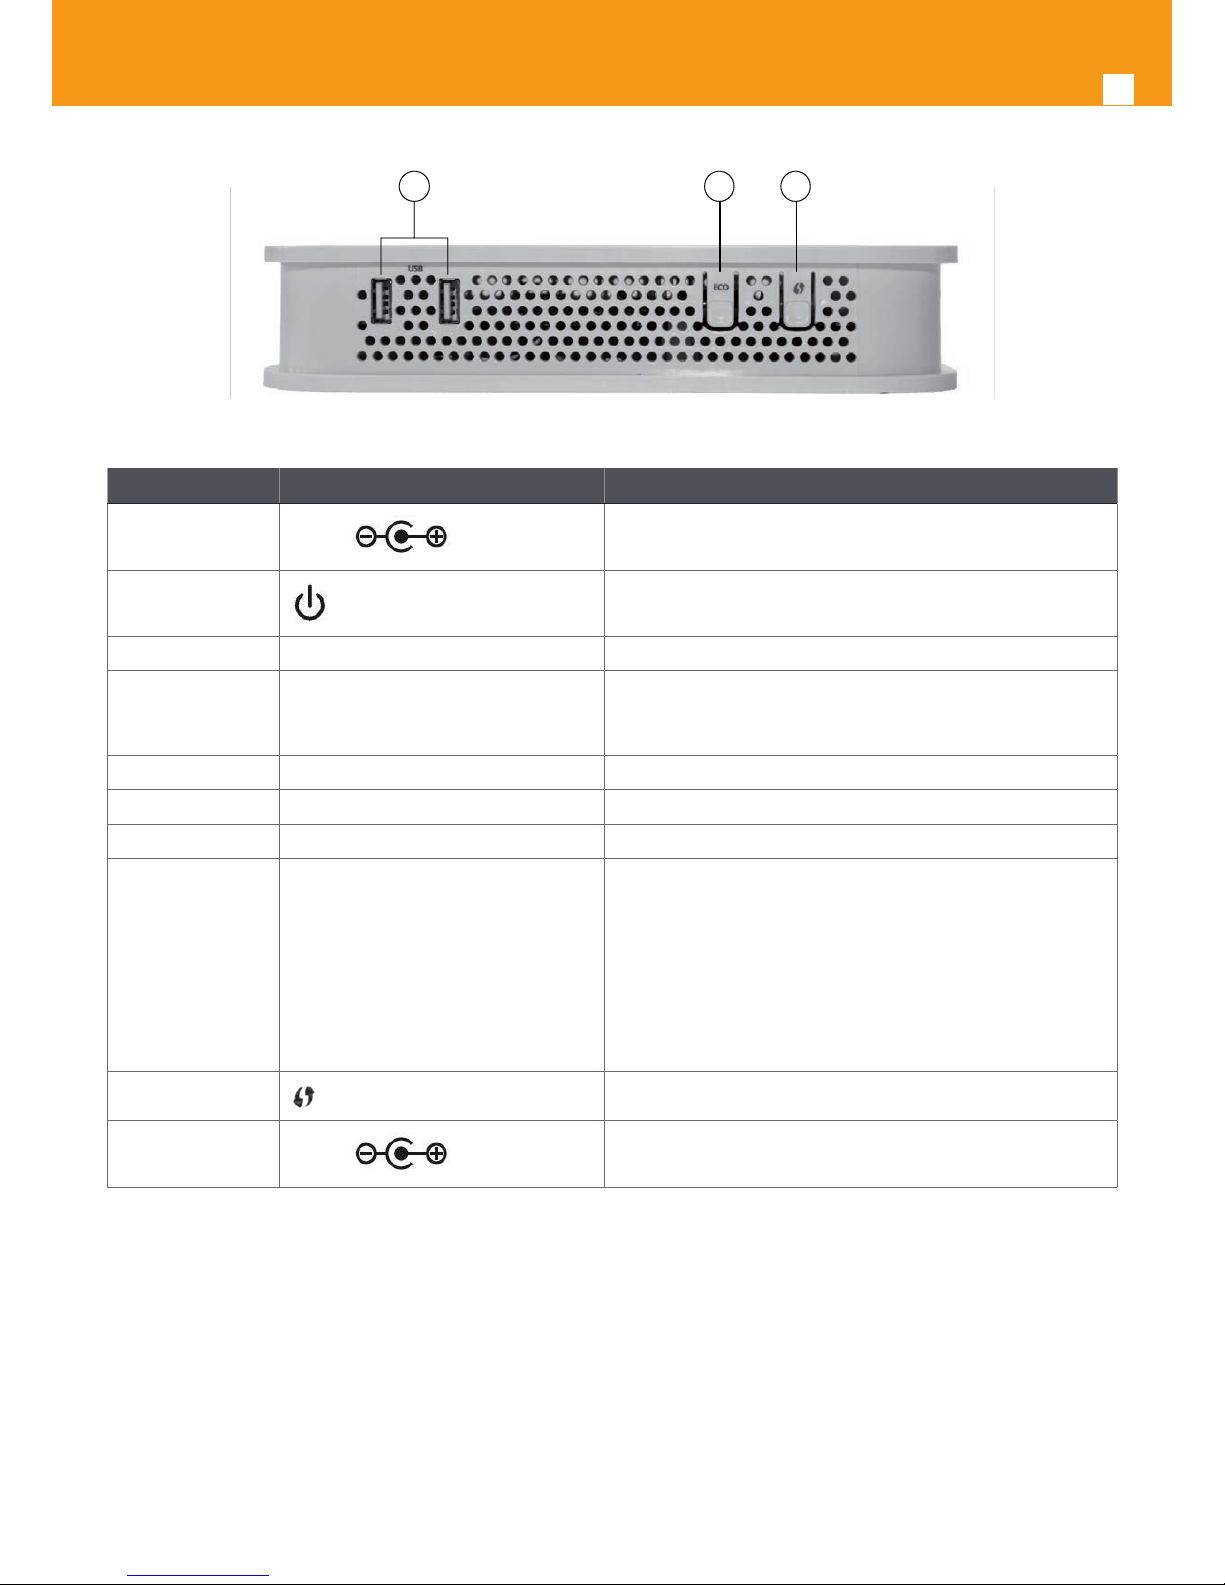
8 9
7
Figure 4-3: Refs. 769501-769502 connections 2
Number Name Description
1
12V
12V DC Power Supply Connector
2
ON/OFF button
3 FXS (1, 2) 2x RJ11 – FXS Ports
4 LAN (1, 2, 3, 4)
4x RJ45 Ports - 10/100/1000Base-T
Ethernet with AUTO-MDIX
5
(1)
RF Video
(1)
Video RF Connector, F type
(1)
6 RST Congurations RESET button
7 USB (1, 2) 2x USB 2.0 ports
8 ECO
Energy saving button.
In order to verify the status of all LEDS press the button.
If not pressed only POWER and RADIO SIGNAL LEDs have updated status information.
9
WPS - WI-FI Protected Set-up
7
12V
12V DC Power Supply Connector
Table 4-1: Refs. 769501-769502 connections description
NOTES:
(1) Optional ;
Dependent on the Refs. 769501-769502 specic model
Page 33
EN
33
4.3 How to Setup Refs. 769501-769502
The Refs. 769501-769502 may be installed horizontally on a at surface or wall mounted. Quick steps for these setups are described below.
Wall-mount
Refs. 769501-769502 wall mounting kit consists of two AGL. ZN. CC. PZ. 3,5X30mm screws, standard DIN 7505-B and two Nylon M 6X30 wall anchors.
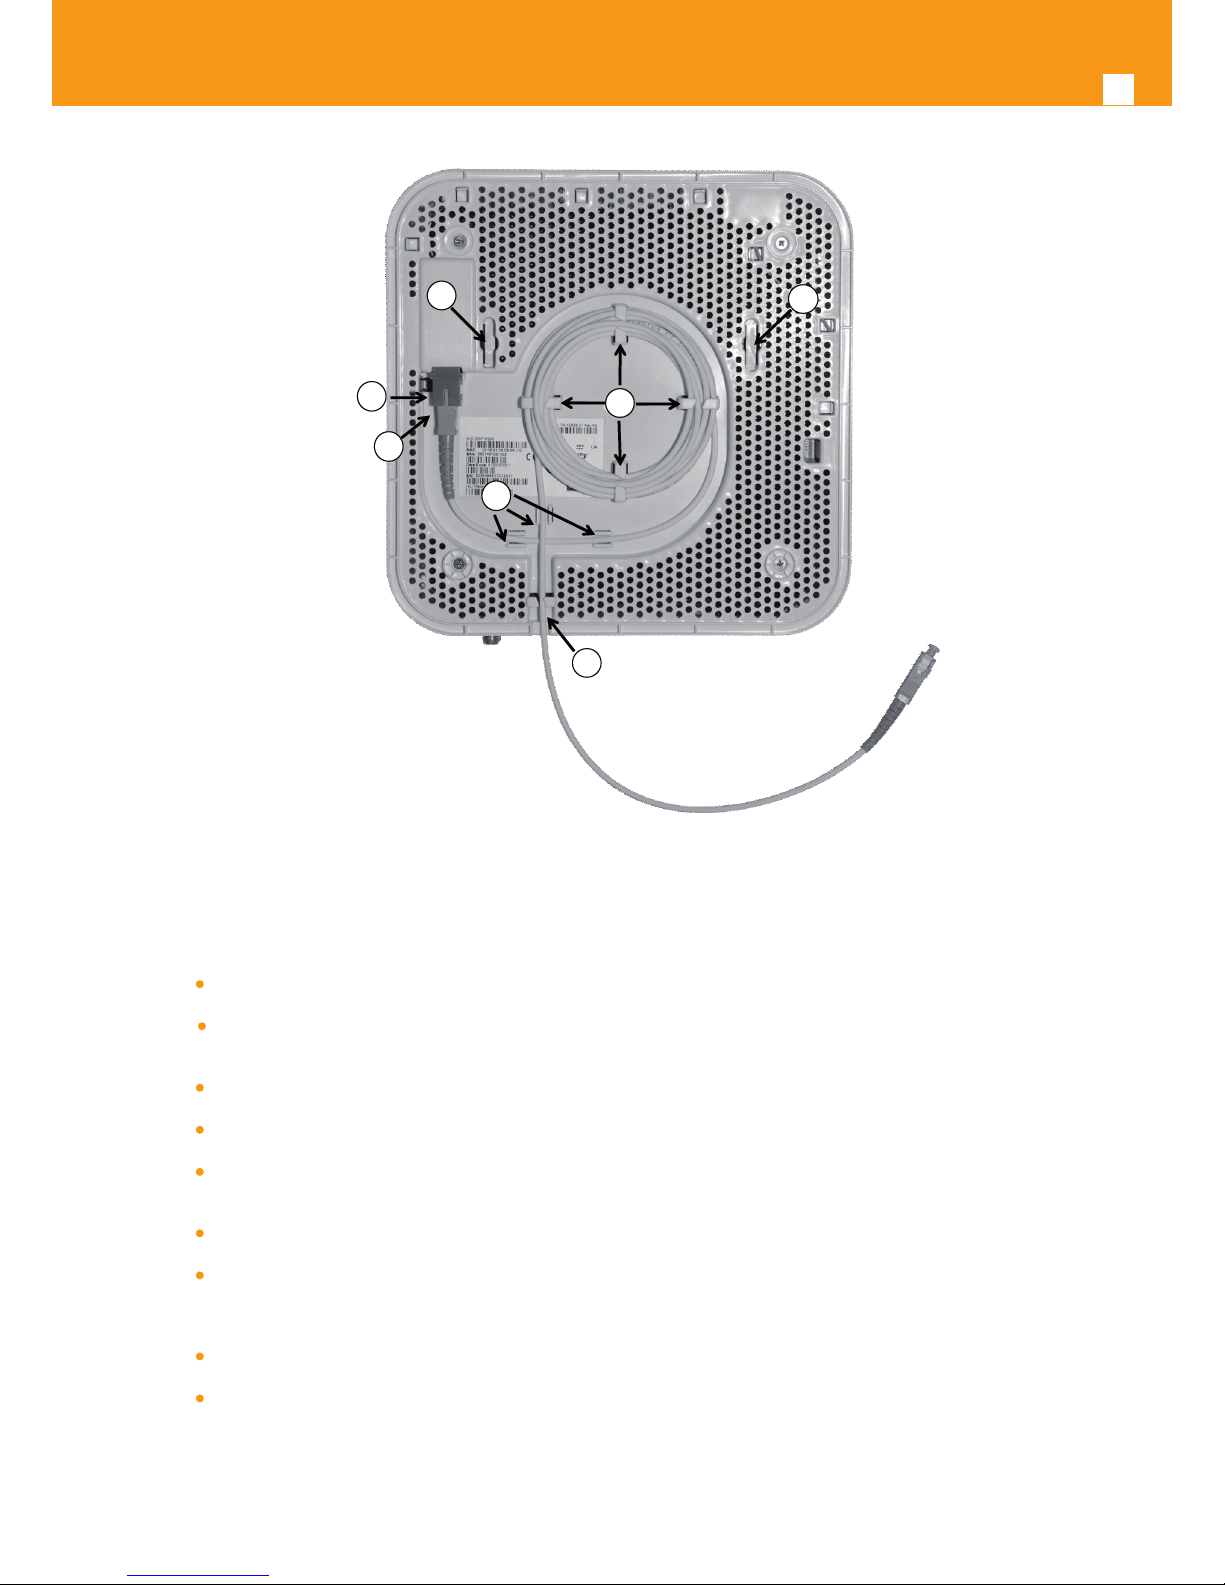
On the back of the Refs. 769501-769502 there are two mounting hole. Refer to Figure 4-4- a) to locate the mounting holes for your
installation;
Mark on the wall the two Refs. 769501-769502 holding screws’ locations;
Drill the holes on the wall with a drill bit size that matches the screws or wall anchors’ size if you are using wall anchors;
Secure the screws on the wall leaving a distance of about 3mm between the screw nut and the wall;
Remove the Refs. 769501-769502 optical adaptor protection cap, Figure 4-4- b);
Clean the Refs. 769501-769502 optical connector face within the optical adaptor with an appropriate optical connector cleaning
material;
Remove the protection cap of one of optical SC/APC connector of optical patchcord;
Clean the optical SC/APC connector face with an appropriate optical connector cleaning material;
Plug the patchcord cleaned SC/APC optical connector on the Refs. 769501-769502 SC/APC adaptor, observing the alignment
mechanism, Figure 4-4- c);
You will hear a click when the connector is secure into place;
Pass the optical patchcord, in a counter- clockwise direction, round the storage circular guide on the back of the equipment, wrap-
ping it round as many times as necessary, Figure 4-4- d). Please avoid small bend radius on the patchcord (30mm minimum bend
radius);
Pass the other end of the optical patchcord to the outside of the equipment using the passing hole, Figure 4-4- f );
Fix the optical patchcord with plastic clamps to the Refs. 769501-769502 the appropriate xing support fastening the plastic clamp
just enough to secure the optical patchcord, Figure 4-4- e);
Hold the Refs. 769501-769502 vertically and align the center of the equipment mounting holes Figure 4-4- a) with the holding
screws in the wall;
Assure the screws enter the mounting holes, Figure 4-4- a);
Slide the equipment vertically down to hold it in place.
Page 34
34
GPON ONT
a
a
b
d
e
f
c
Figure 4-4: Refs. 769501-769502 back side –optical patch cord installation
Horizontal position
Remove the Refs. 769501-769502 optical adaptor protection cap, Figure 4-4- b);
Clean the Refs. 769501-769502 optical connector face within the optical adaptor with an appropriate optical connector cleaning
material;
Remove the protection cap of one of optical SC/APC connector of optical patchcord;;
Clean the optical SC/APC connector face with an appropriate optical connector cleaning material;
Plug the patchcord cleaned SC/APC optical connector on the Refs. 769501-769502 SC/APC adaptor, observing the alignment
mechanism, Figure 4-4- c);
You will hear a click when the connector is secure into place;
Pass the optical patchcord, in a counter- clockwise direction, round the storage circular guide on the back of the equipment, wrap-
ping it round as many times as necessary, Figure 4-4- d). Please avoid small bend radius on the patchcord (30mm minimum bend
radius);
Pass the other end of the optical patchcord to the outside of the equipment using the passing hole, Figure 4-4- f );
Fix the optical patchcord with plastic clamps to the Refs. 769501-769502 the appropriate xing support fastening the plastic clamp
just enough to secure the optical patchcord, Figure 4-4-e).
Page 35
EN
35
4.4 Interface connection
4.4.1 Optical cable connection
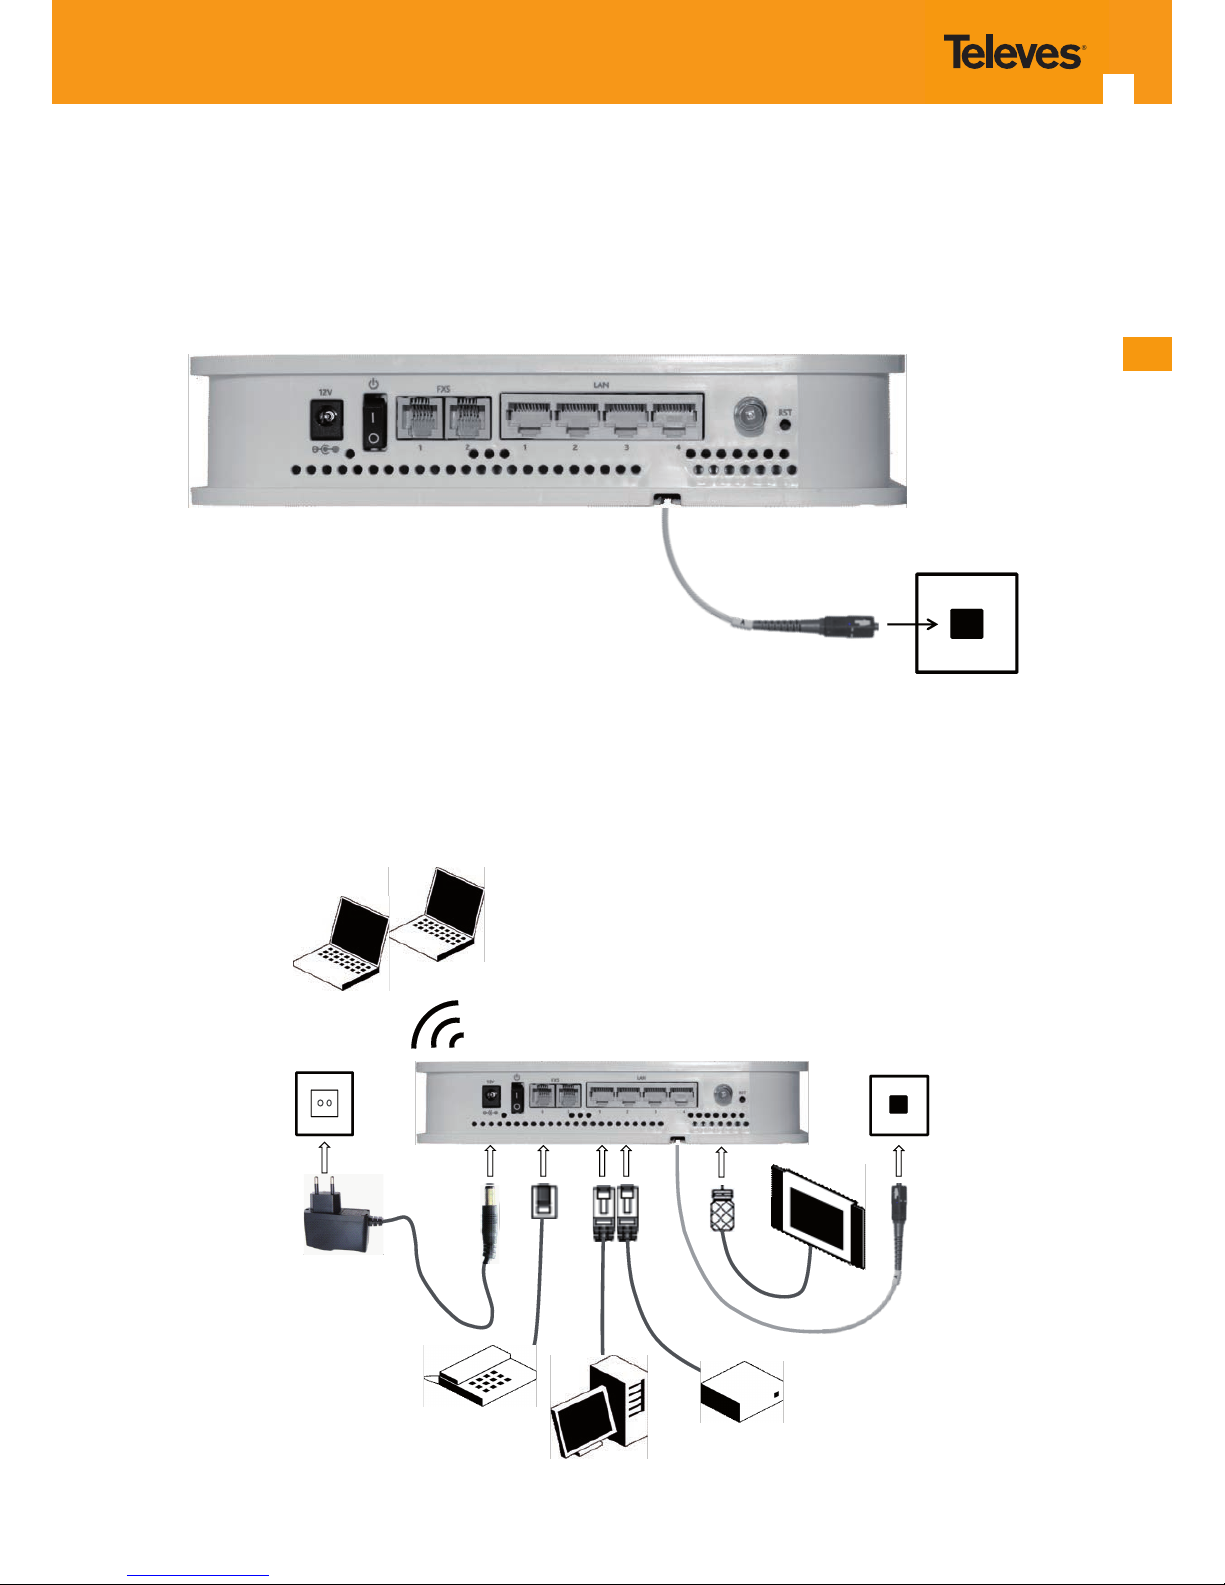
Connect the optical cable (C1) from the Refs. 769501-769502 to the optical socket, Figure 4-5;
Optical
wall socket
C1
Figure 4-5: Interfaces connection (PON Interface)
4.4.2 General Overview of Refs. 769501-769502 Connections
Figure 4-6 below shows the connections to be made between the Refs. 769501-769502 and the home network devices. Please refer to Figure 4-1
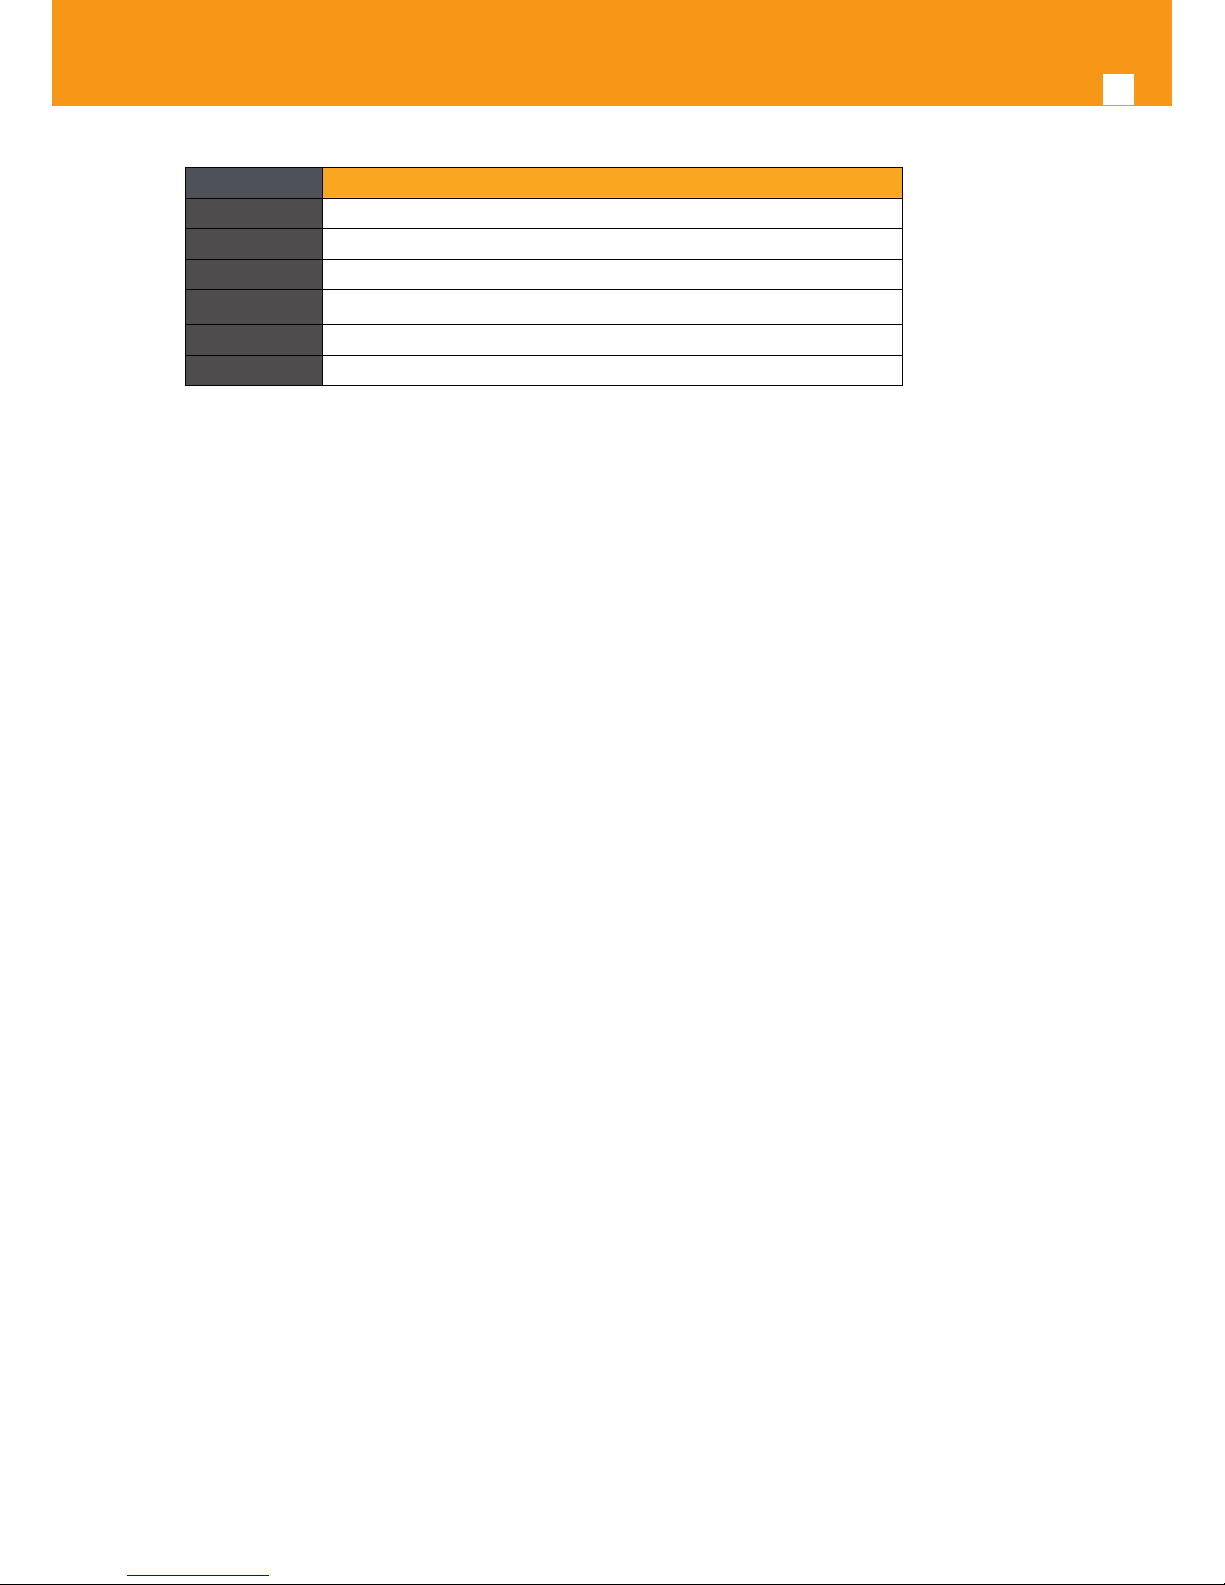
and 4-1 for the Refs. 769501-769502 connector description and to Table 4-2 for the description of the connecting cables that must be used.
Optical
wall socket
Laptops
PC
SETOP BOX
Telephone/Fax
220V/110 V
AC
ONT-RGW Rear View
C4
C3
C3
C2
C1
W1
C5
TV
Figure 4-6: Refs. 769501-769502 connections
Page 36
36
GPON ONT
Connection Description
C1
12V DC Adapter
C2
RJ11 Telephone cable
C3
Ethernet Cable UTP CAT56 cable (direct or crossover)
C4
Single-mode Optical Cable with SC/APC Connector (GPON)
C5 (1)
Cable with F-type Connectors, Coaxial 75 Ohm
W1
WI-FI
NOTES:
(1) Optional ;
Dependent on the Refs. 769501-769502 specic model
Table 4-2: Refs. 769501-769502 connections
Page 37
EN
37
5. Conguration
5.1 Refs. 769501-769502 activation
The Refs. 769501-769502 activation process has a distributed set of procedures that allow the connection of an inactive equipment to a PON network. This conguration is done following the procedure described in the OMCI protocol.
5.2 Customization
For customization process, the requirements specied in the G.984.4, G.984.5 and ‘Implementer’s Guide’ in the G.984.4 v1 are taken into account.
5.2.1 Software download from the OLT
The software download is made following the OMCI-based procedure included in the ‘Implementer’s Guide’ of the G.984.4 Recommendation.
The Managed Entity (ME) in charge of managing the software download is named Software Image. Per each ME containing independently-manageable software, the Refs. 769501-769502 creates two software images. Each image will have three attributes:
Valid - if it has been veried that it’s content is an image with executable code;
Committed - if once the Refs. 769501-769502 is rebooted, it is loaded and executed;
Active - if it is loaded and it is being executed in the Refs. 769501-769502.
There can be only one active image and only one commited image at a given moment. The Refs. 769501-769502 goes through a series of states in
order to download and activate a software image. Each state is dened according to the states of the variables of both images. The OLT controls
the Refs. 769501-769502 state through a series of commands:
Start downloaad
It starts the software download sequence. This action is only valid for inactive and non-commited software images;
Download section
It downloads a section of a software image. This action is only valid for an image that is being downloaded;
End download
It indicates the end of a download sequence, providing the CRC and information about version for the nal verication of the
downloaded software image. This action is only valid for a software image that is being downloaded;
Activate image
It loads/executes a valid software image. When this action is applied to an inactive software image, the execution of the current
code image is suspended, the associated software image is loaded from the non-volatile memory and the execution of the
new code image is started. When this action is applied over a software image that is active, a reboot is executed;
Commit image
It selects a valid SW image to be loaded and executed by default when the Refs. 769501-769502 is restarted;
Composition of the Software Image
A software image is divided into sections of 31 bytes, with one section per OMCC message and each section protected by the
CRC of the OMCC. A group of sections makes up a window, and a group of windows constituting the image.
Page 38
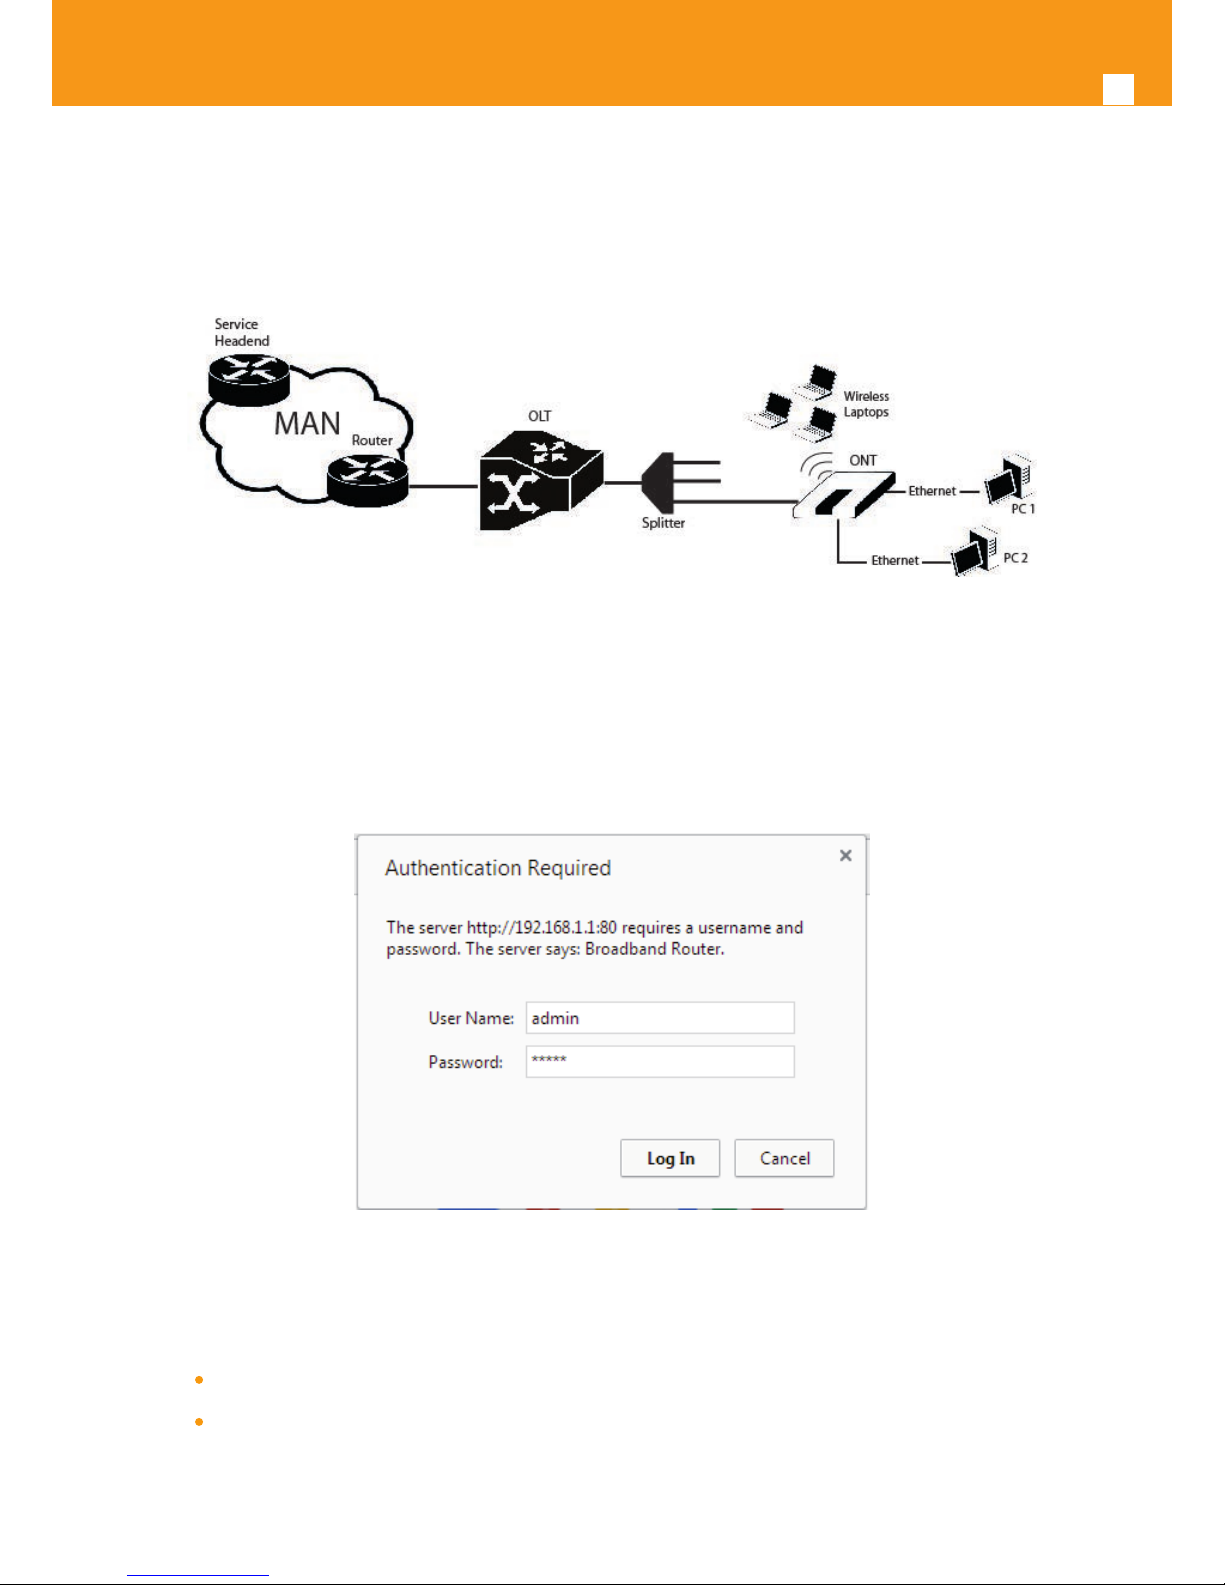
38
GPON ONT
5.3 Network Setup
Refs. 769501-769502 is the link between the modem and all of the peripherals in the LAN. The following gure shows a possible network setup
containing three wireless computers and two wired computers.
Figure 5-1: Refs. 769501-769502 Network Setup
5.4 Refs. 769501-769502 General Management Conguration
To congure the Refs. 769501-769502, enter the URL address http://192.168.1.1 address in an internet browser.
Figure 5-2: Refs. 769501-769502 management login
The administrative user and password is:
User: admin
Password: admin
After logging in, the main window is as shown in the next gure. The shown main window is device info summary window..
Page 39
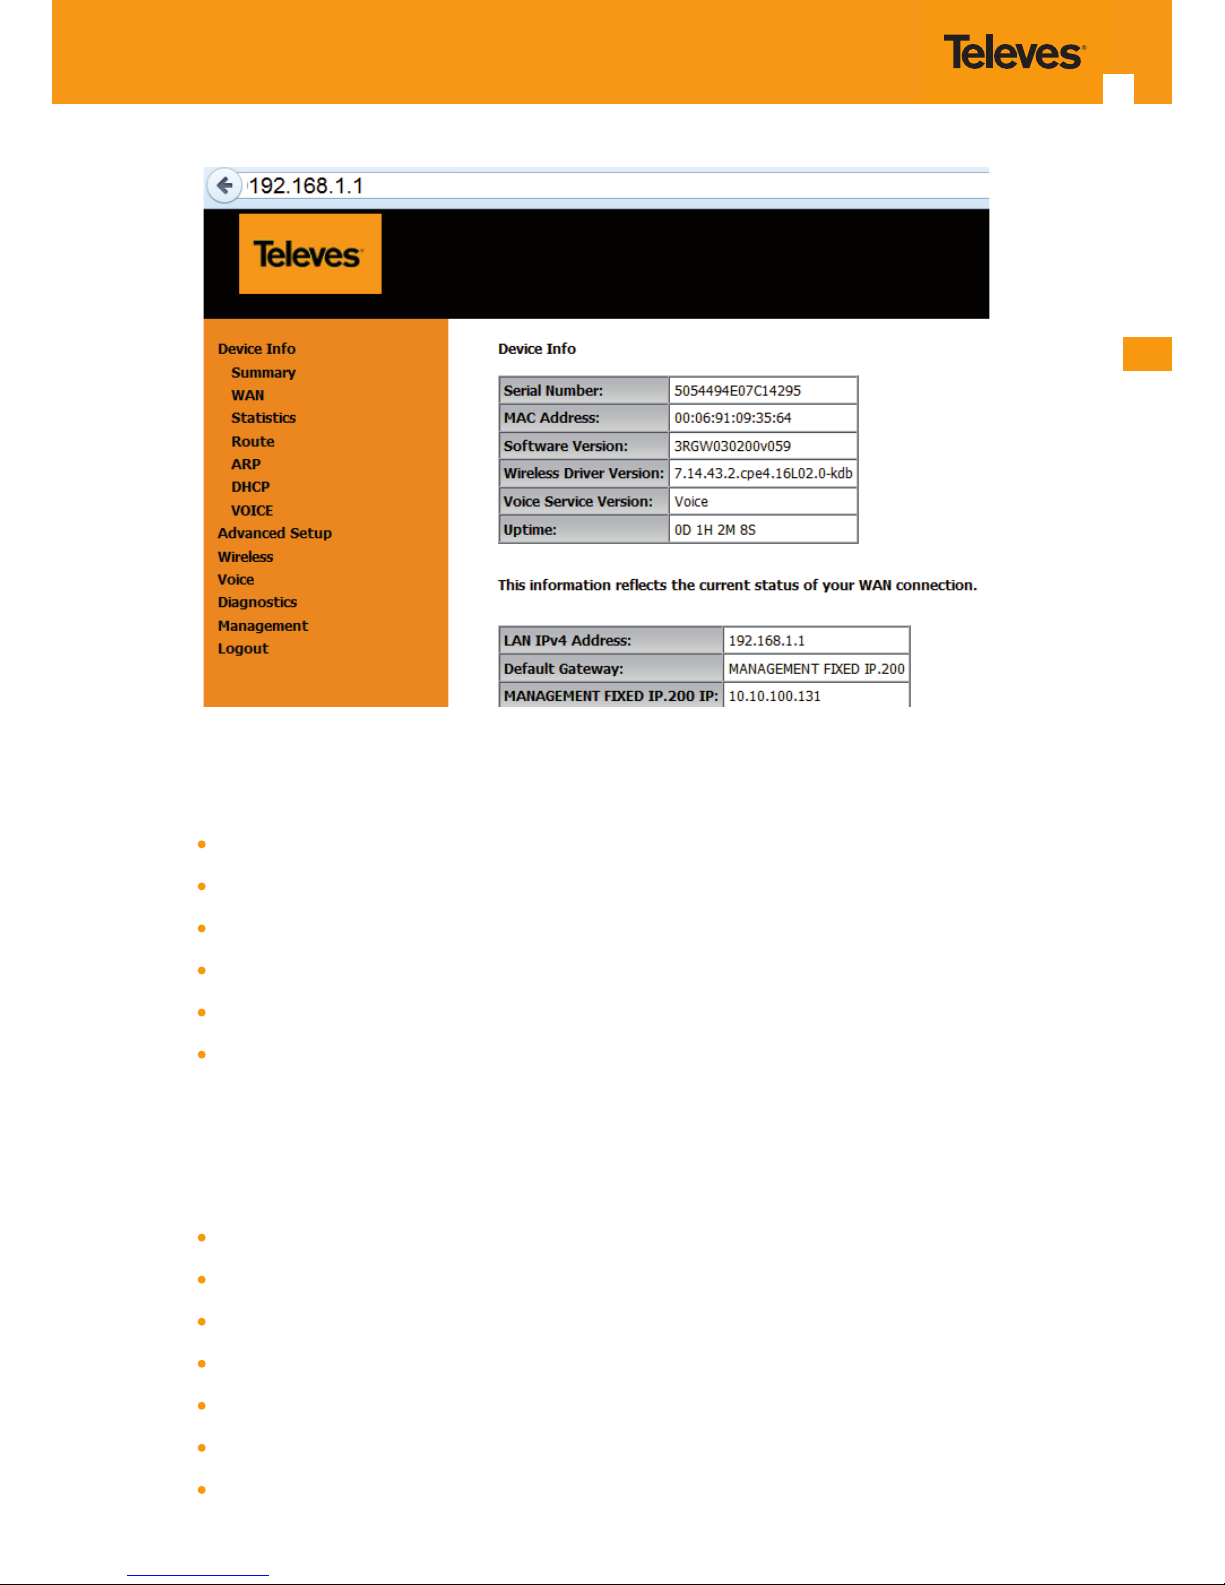
EN
39
Figure 5-3: Refs. 769501-769502 management main screen
The Refs. 769501-769502 Management lets the user congure these categories by clicking the folder icons in the Control Menu pane.
Device Info
Advanced Setup
Wireless
Voice
Diagnostics
Management
5.5 Device Info
Selecting Device Info menu item, expands Device Info sub-menu into listed items, Figure 5-4:
Summary
WAN
Statistics
Route
ARP
DHCP
VOICE
Page 40
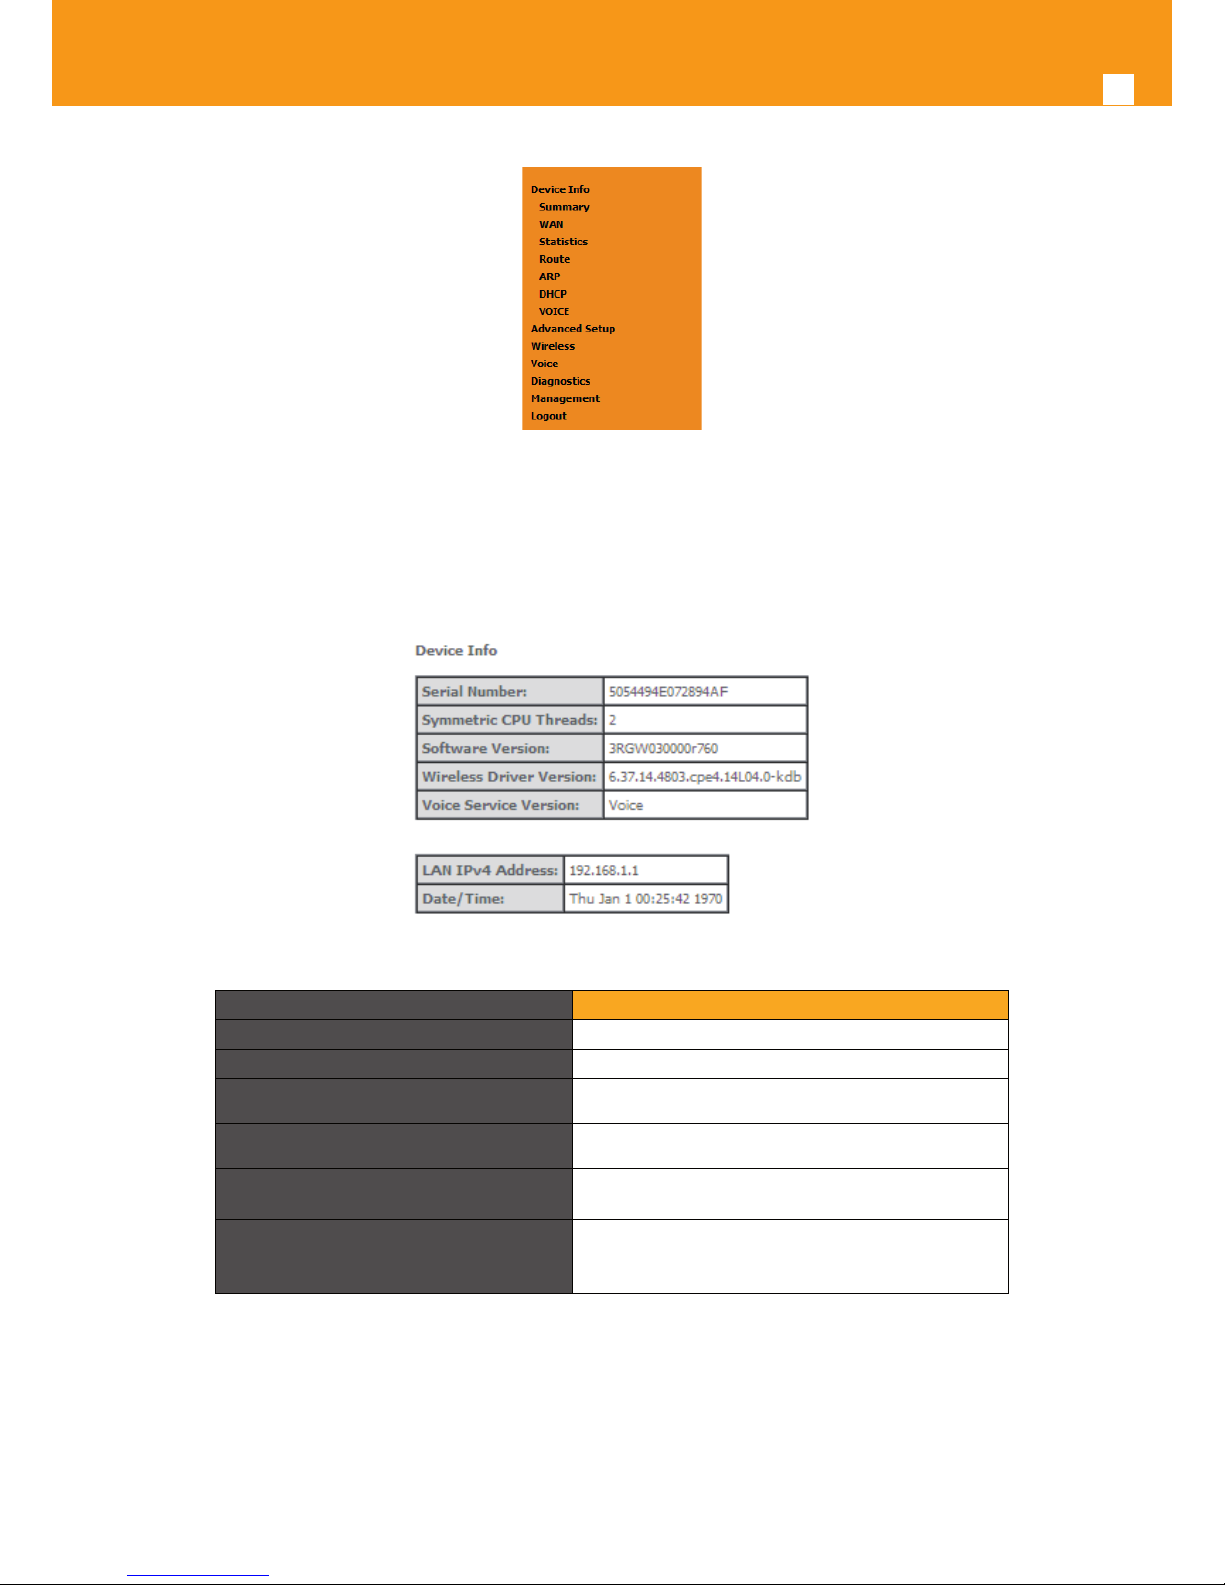
40
GPON ONT
Figure 5-4 : Refs. 769501-769502 Graphic User Interface main menu
5.5.1 Summary
Selection of Device Info sub-menu item Summary, displays in the main window the initial device info conguration details, Figure 5-5. The initial
displayed information will be updated to the current device info details by the performed conguration settings of the ONT. Description of the
Device Info window parameters can be found in Table 5-1
Figure 5-5: Device Info details – initial conguration
Parameter Description
Serial Number ONT serial number
Symmetric CPU Threads Number of ONT Symmetric CPU Threads
Software Version Installed ONT software version
Wireless Driver Version Installed ONT Wireless Driver version
LAN IPv4 Address
ONT LAN initial IPv4 Address; corresponds to the
ONT IPV4 address used to access the ONT HTTP GUI
Date/Time
Initial ONT date; this value will be updated the ONT
has access to an NTP server, upon an IPoE conguration
Table 5-1: Device Info window parameters
Page 41
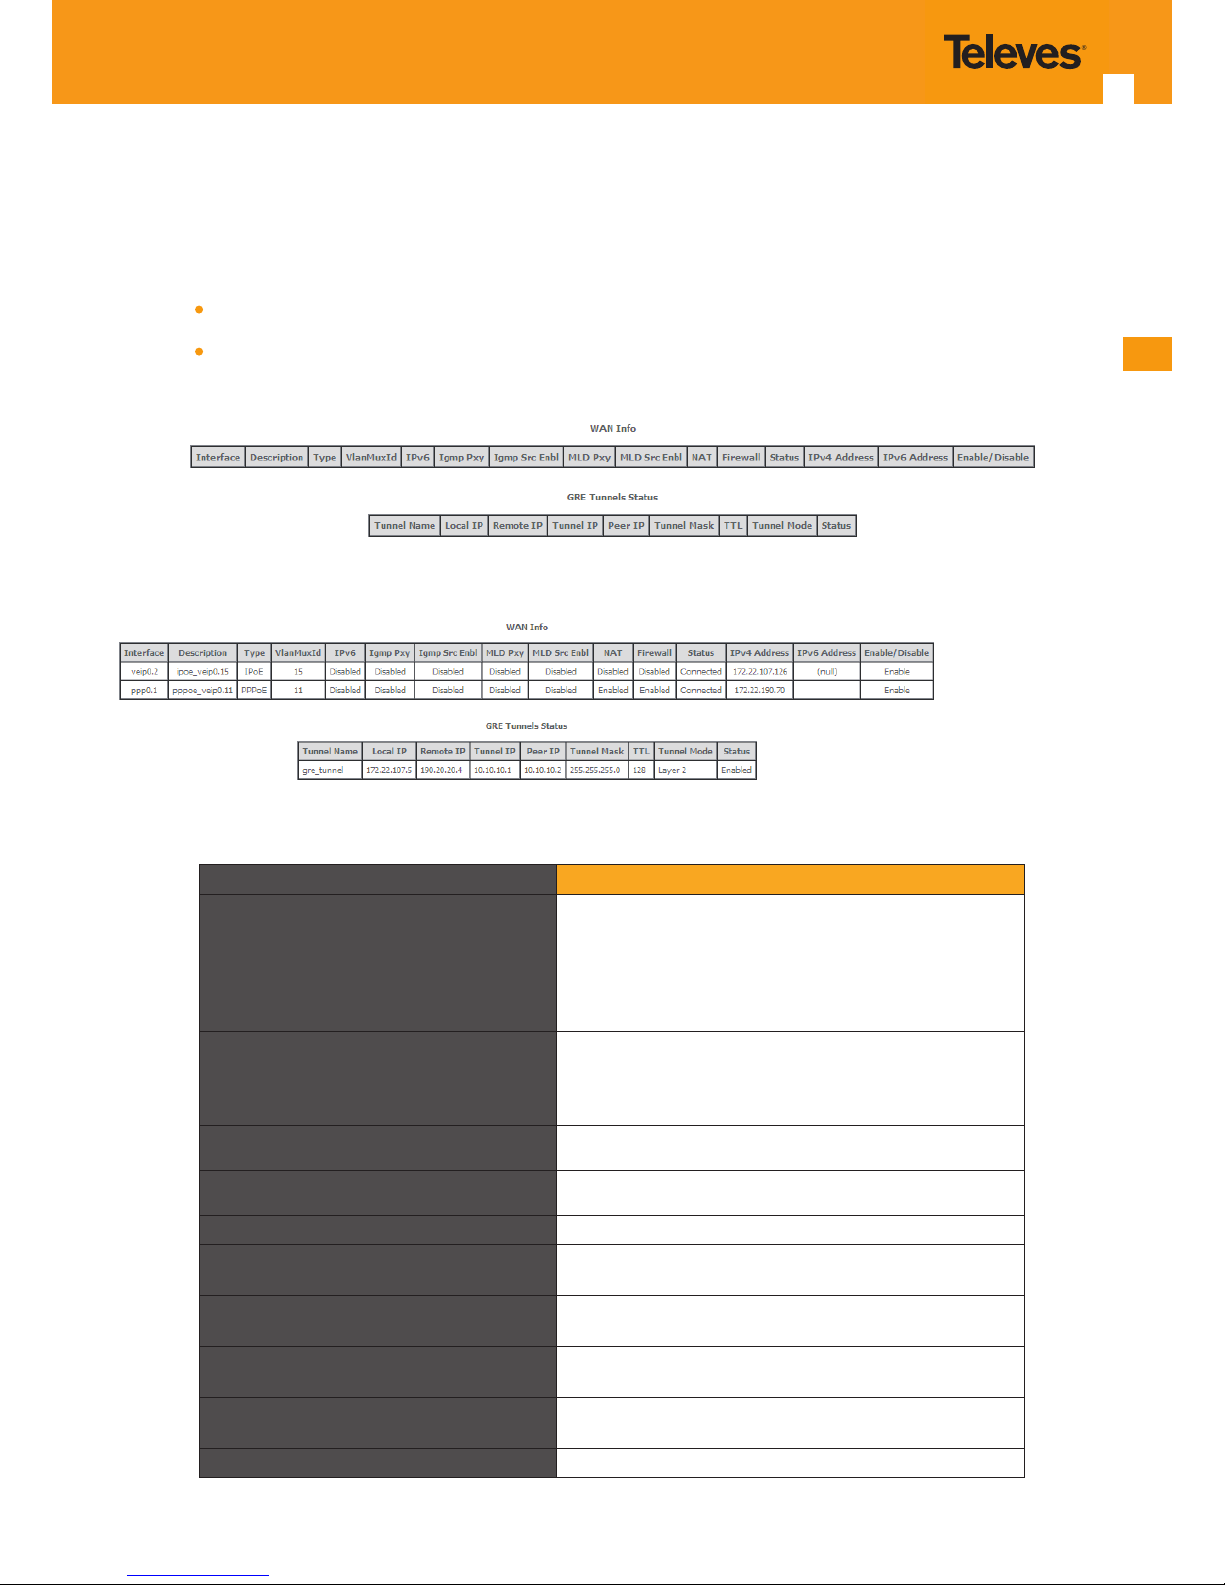
EN
41
5.5.2 WAN
Selection of the Device Info sub-menu item WAN displays in the main window the current WAN conguration details, Figure 5-6.
The window is composed of two tables:
WAN info;
GRE Tunnels Status
Description of the WAN Info Table parameters can be found in Table 5-2 and GRE Tunnels Status table parameters in.Table 5-3.
Figure 5-6: WAN current conguration details window – initial window
Figure 5-7: WAN current conguration details window – example of 2 WAN interfaces and a GRE Tunnel congured
Parameter Description
Interface
WAN interface identication (string); attributed on the
Wan interface conguration; if not set by the user, the
system names the interface automatically as “xxx0.n/”,
where xxx is the type of interface (eg ppp stands for pppoe) n is number indicating order of interface creation,
starting in 1
Description
WAN service description; String that can be entered by
the user; default values indicates type of WAN service
(pppoe/ipoe/gre/br), used layer 2 interface (eg. veip0/
eth1) interface and used vlan id (eg. 11)
Type Identies Wan service Type (PPPoE/IPoE/gre/br)
VlanMuxId Used 802.1Q VLAN ID (0-4094)
IPv6 Flag (enable/disable) ; indicates if IPv6 is enabled
Igmp Pxy
Flag (enable/disable) ; indicates if IGMP proxy is enabled;
to use for multicast conguration in the case of IPv4.
Igmp Src Enbl
Flag (enable/disable); indicates if IGMP source is enabled;
to use for multicast conguration in the case of IPv4.
MLD Pxy
Flag (enable/disable) ; indicates if MLD proxy is enabled;
to use for multicast conguration in the case of IPv6.
MLD Src Enbl
Flag (enable/disable) ; indicates if MLD source is enabled;
to use for multicast conguration in the case of IPv6.
NAT Flag (enable/disable); Indicates if NAT is enabled
Table 5-2: WAN Info Table parameters
Page 42
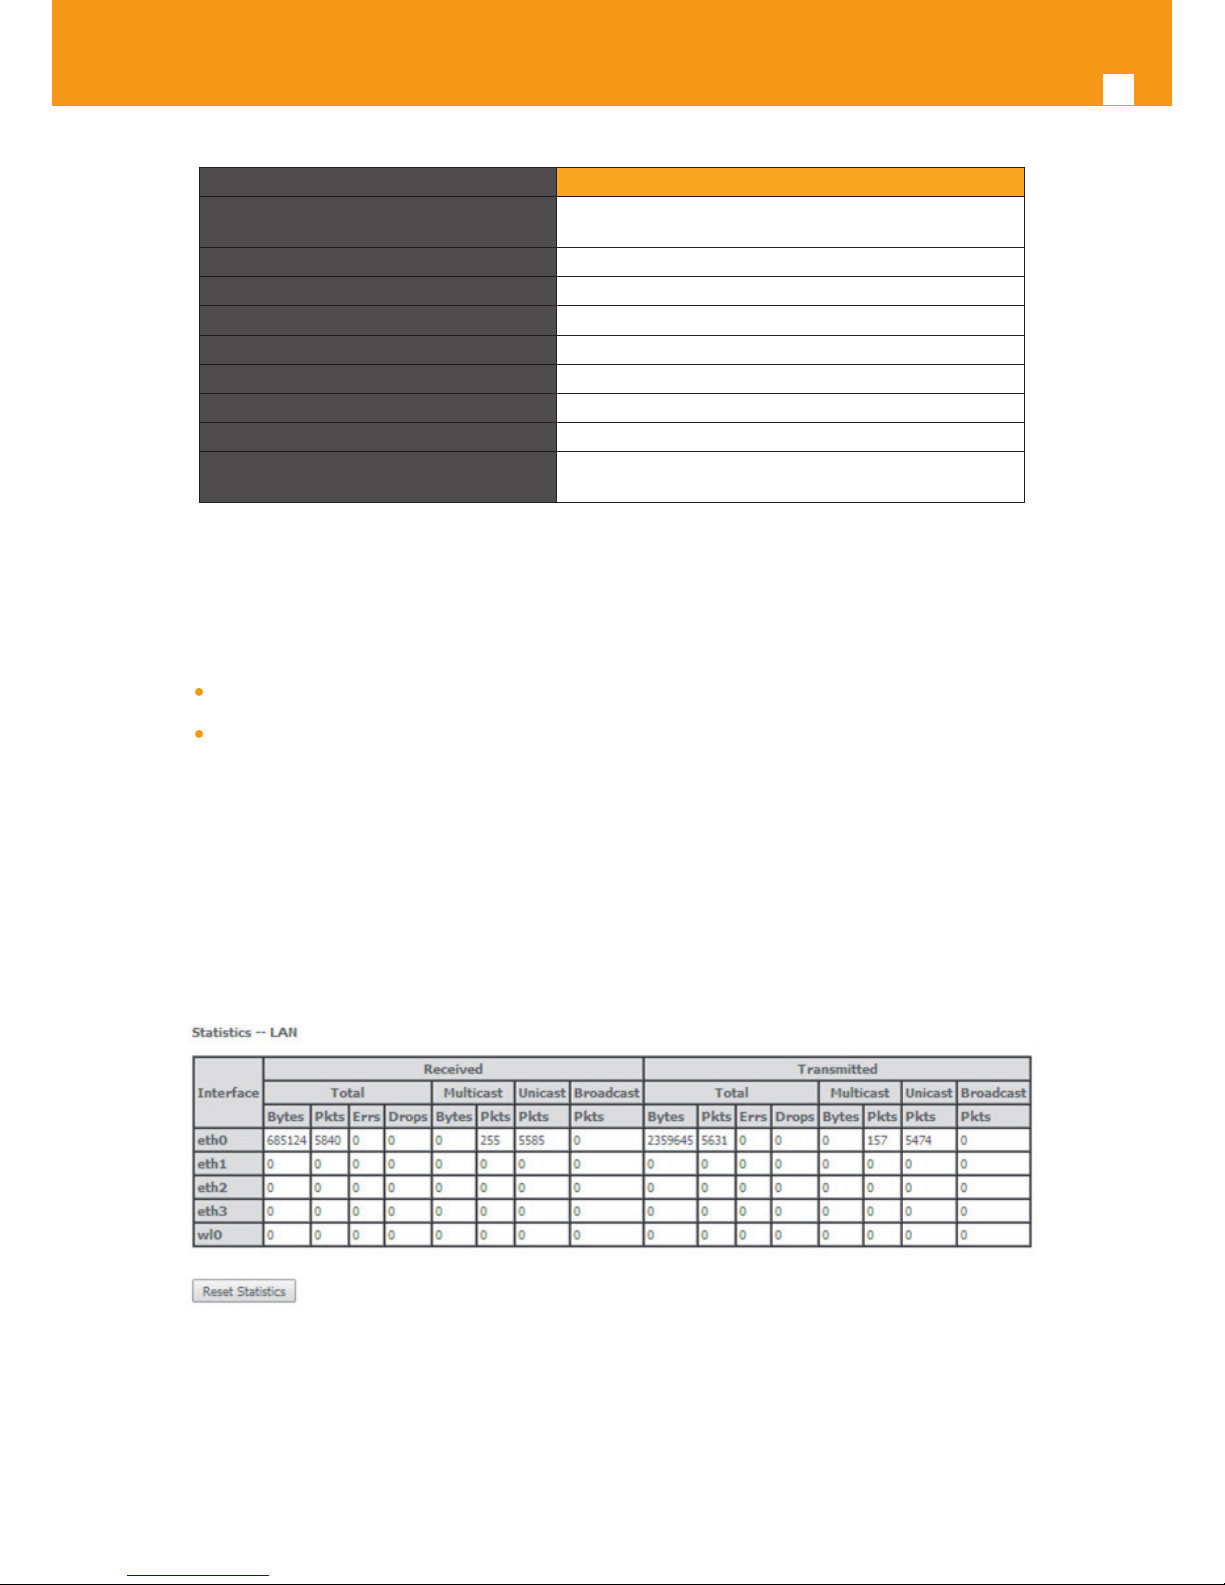
42
GPON ONT
Parameter Description
Tunnel Name
Gre Tunnel identication (string) congured when gre
tunnel is created
Local IP IP address of the local end interface of the GRE tunnel
Remote IP IP address of the local end interface of the GRE tunnel
Tunnel IP Tunnel IP Address
Peer IP Peer IP Address
Tunnel Mask Tunnel mask
TTL Time To Live in seconds
Tunnel Mode Indicates if this is a Layer 2 mode tunnel
Status
Flag (enable/disable); indicate the Tunnel is administra-
tively enabled
Table 5-3: GRE Tunnels Status Table parameters
5.5.3 Statistics
When selected the Device Info sub-menu item Statistics expands into a statistics sub-menu, composed of the following items:
LAN
WAN Service
The main window shows the LAN statistics information.
5.5.3.1 LAN
Selection of the Device Info, Statistics submenu, item LAN displays in the main window the current LAN (Local Area Network) statistics information,
Figure 5-8.
Received and Transmitted Total and per type of trac Statistics will be displayed for each LAN interface with trac. LAN statistics parameter description can be found in Table 5-4.
Figure 5-8: LAN Statistics
Page 43
EN
43
Parameter Description
Interface
LAN interface Identication (string).
eth #, # - number : 0 to 3 – Refs. 769501-769502
ETH port number
wl0, Wireless interface
Total
Received/transmitted
Total values (Multicast+Unicast+Broadcast) of:
Bytes – Total number of Received /Transmitted
Bytes
Pkts – Total number of Received/transmitted
Packets
Errs– Total number of Received/transmitted Errors
Drops – Total number of Received/transmitted
Drops
Multicast
Received/transmitted
Number of received/transmitted Multicast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Unicast
Received/transmitted
Number of received/transmitted Unicast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Broadcast
Received/transmitted
Number of received/transmitted Broadcast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Table 5-4: LAN Statistics Table parameters
Page 44
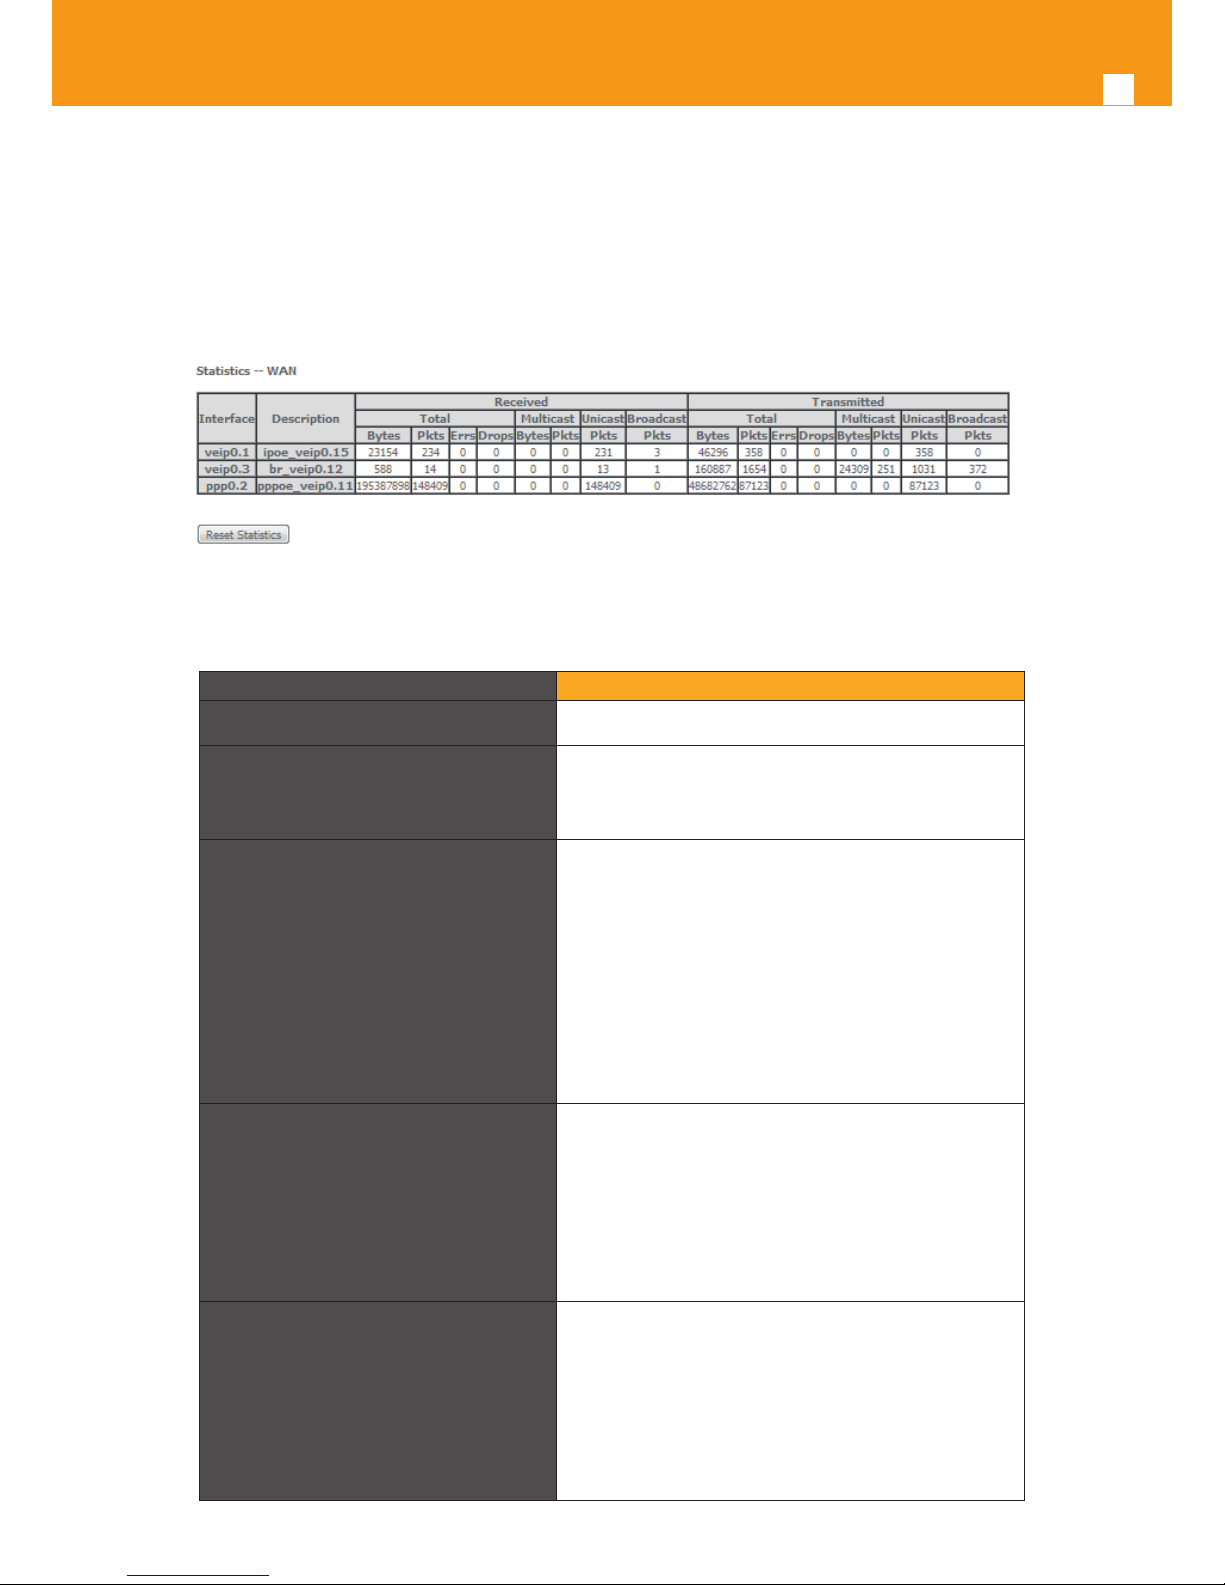
44
GPON ONT
5.5.3.2 WAN Service
Selection of the Device Info, Statistics sub-menu Item WAN service displays in the main window the Wide Area Network statistics information per
congured Wan service, Figure 2-1.
WAN Service statistics parameter description can be found in Table 5-2.
Figure 5-9: WAN Statistics
Parameter Description
Interface WAN interface identication (string)
Description
WAN service description; String that can be entered by the
user at the Wan service creation ; default values indicates
type of WAN service (pppoe/ipoe/gre/br), used layer 2 interface (eg. veip0/eth1) interface and used vlan id (eg. 11)
Total
Received/transmitted
Total values (Multicast+Unicast+Broadcast) of:
Bytes – Total number of Received /Transmitted
Bytes
Pkts – Total number of Received/transmitted
Packets
Errs– Total number of Received/transmitted Errors
Drops – Total number of Received/transmitted
Drops
Multicast
Received/transmitted
Number of received/transmitted Multicast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Unicast
Received/transmitted
Number of received/transmitted Unicast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Page 45
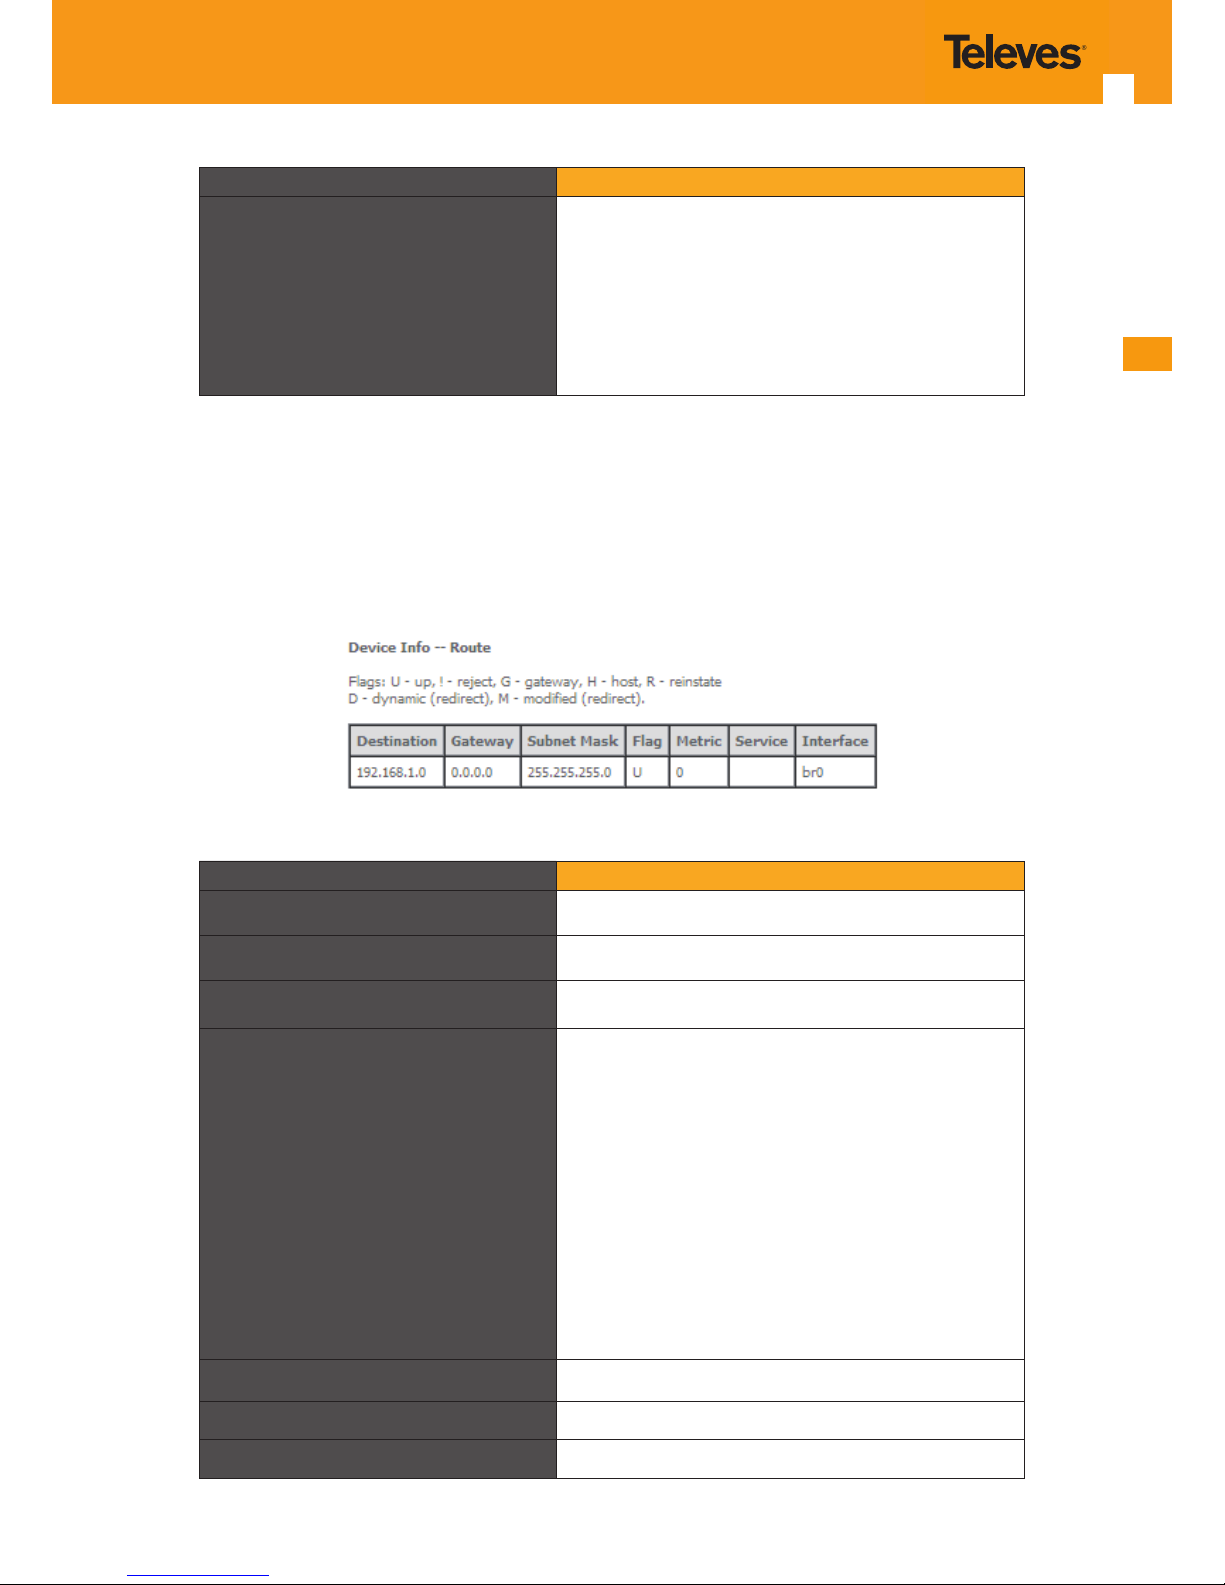
EN
45
Parameter Description
Broadcast
Received/transmitted
Number of received/transmitted Broadcast:
Bytes
Pkts – Packets
Errs– Errors
Drops
Table 5-5: WAN Statistics Table parameters
5.5.4 Route
Selection of the Device Info sub-menu Route item, compresses the open Device info sub-menu if expanded (eg Statistics) and shows in the main
window the Device Routing information, Figure 5-10. In the example bellow the destination address is the address of the Refs. 769501-769502
bridge (br0 Interface) and the route status is up.
Route Table parameter description can be found in Table 5-6.
Figure 5-10: Device Route Info
Parameter Description
Destination IP Destination Address
Gateway Used Gateway IP Address, if congured
Subnet Mask Used sub network mask, if congured
Flag
Route status indication ag:
U – UP
! – reject
G - gateway
H – host
R – Reinstate
D – Dynamic (redirect)
M - modied
Metric Used metric
Service Service using the route
Interface Interface used by the Route
Table 5-6: Device Routing information Table parameters
Page 46
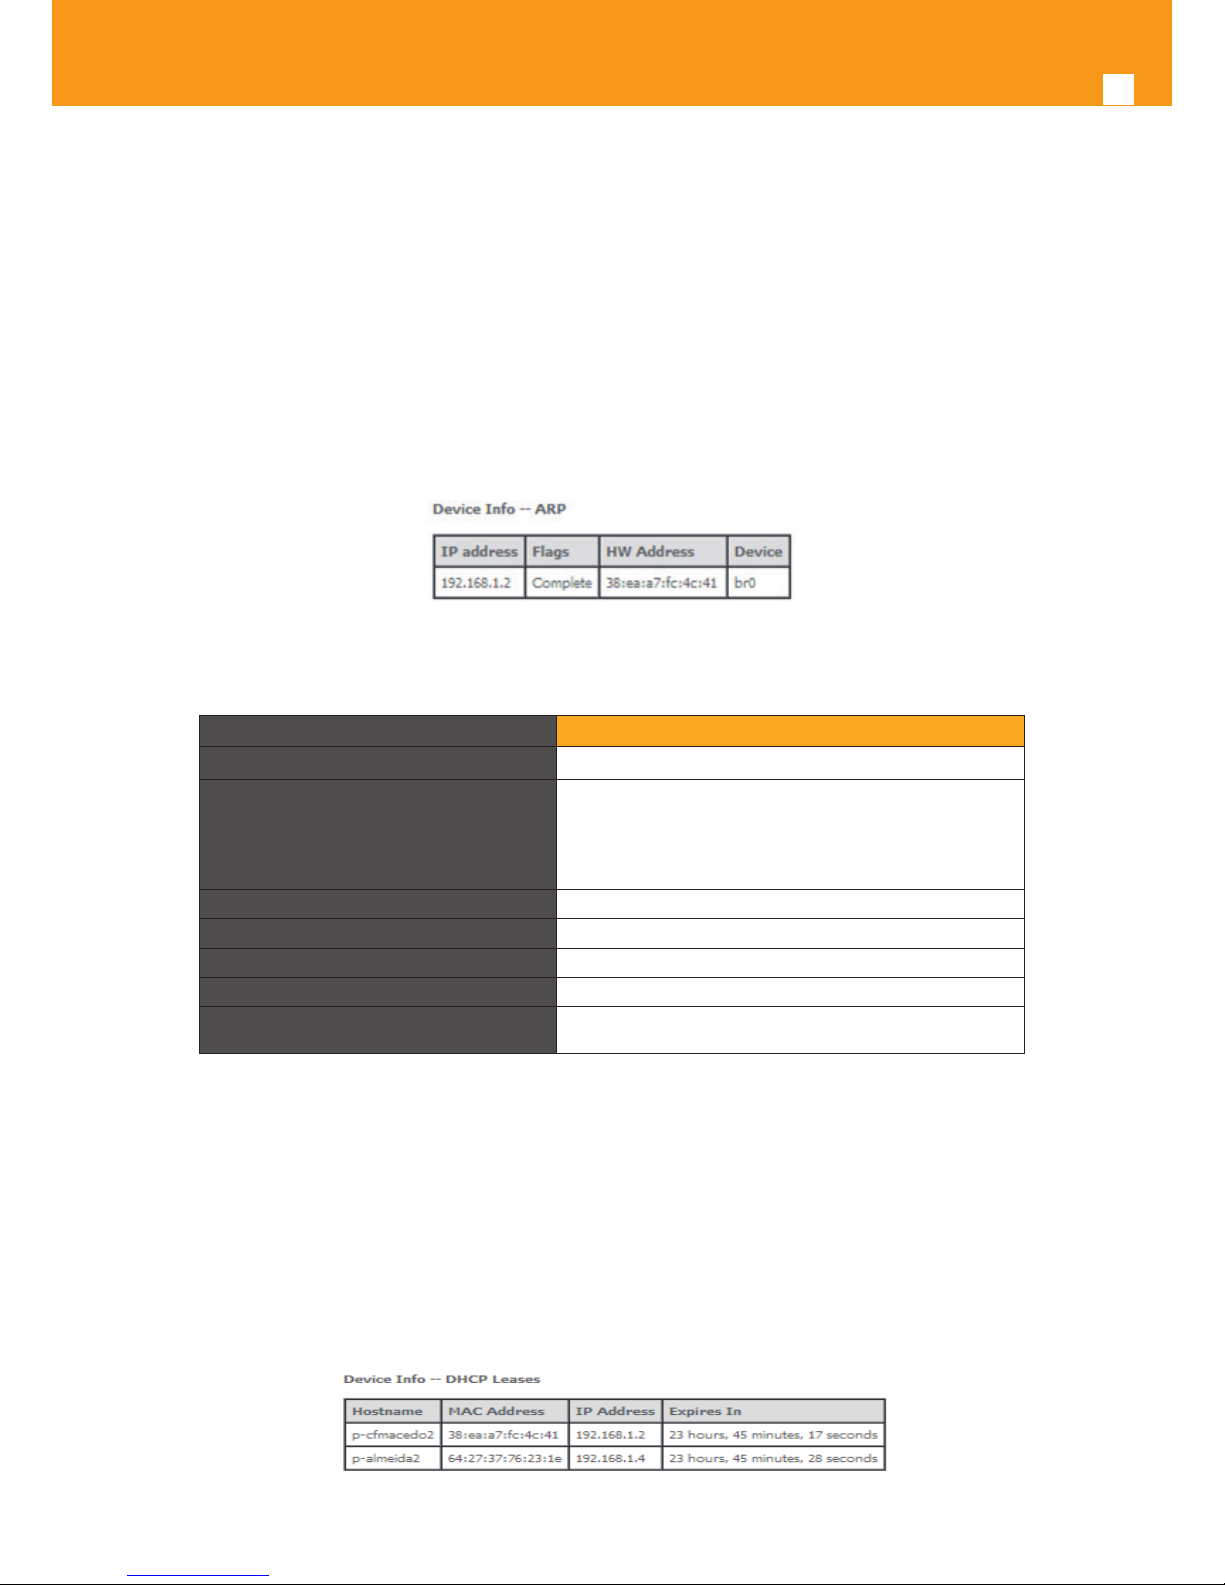
46
GPON ONT
5.5.5 ARP
Selection of the Device Info sub-menu ARP item, compresses the open Device Info sub-menu if expanded (eg Statistics) and shows in the main
window the Device ARP information, Figure 5-11.
Device ARP information parameter description can be found in Table 5-7.
ARP is used to convert an IP address to a Physical address. The ARP table
In the example bellow the IP Address is the allocated IP address by the Refs. 769501-769502 the latop connected to one of the device ETH LAN
ports and used to access the device GUI (Graphic User Interface) for Device conguration. The HW address corresponding to this IP address is the
laptop MAC, the ARP ags value is complete since the IP address was successfully resolved to the Laptop MAC address . The logical device the
laptop is connected is the Refs. 769501-769502 bridge br0. This is the ARP table for this device.
Figure 5-11: Device ARP Info
Parameter Description
IP Address External Device IP Address
Flags
ARP status indication ag:
Complete
Incomplete…
HW address External device Hardware address
Device Used Device Interface
Metric Used Metric
Service Service using the route
Interface Interface used by the route
Table 5-7: Device ARP information Table parameters
5.5.6 DHCP
Selection of the Device Info sub-menu DHCP item, compresses the open Device Info sub-menu if expanded (eg Statistics) and shows in the main
window the Device DHCP Leases information, Figure 5-12.
Device DHCP information parameter description can be found in Table 5-8.
Figure 5-12: Device DHCP Leases Info
Page 47
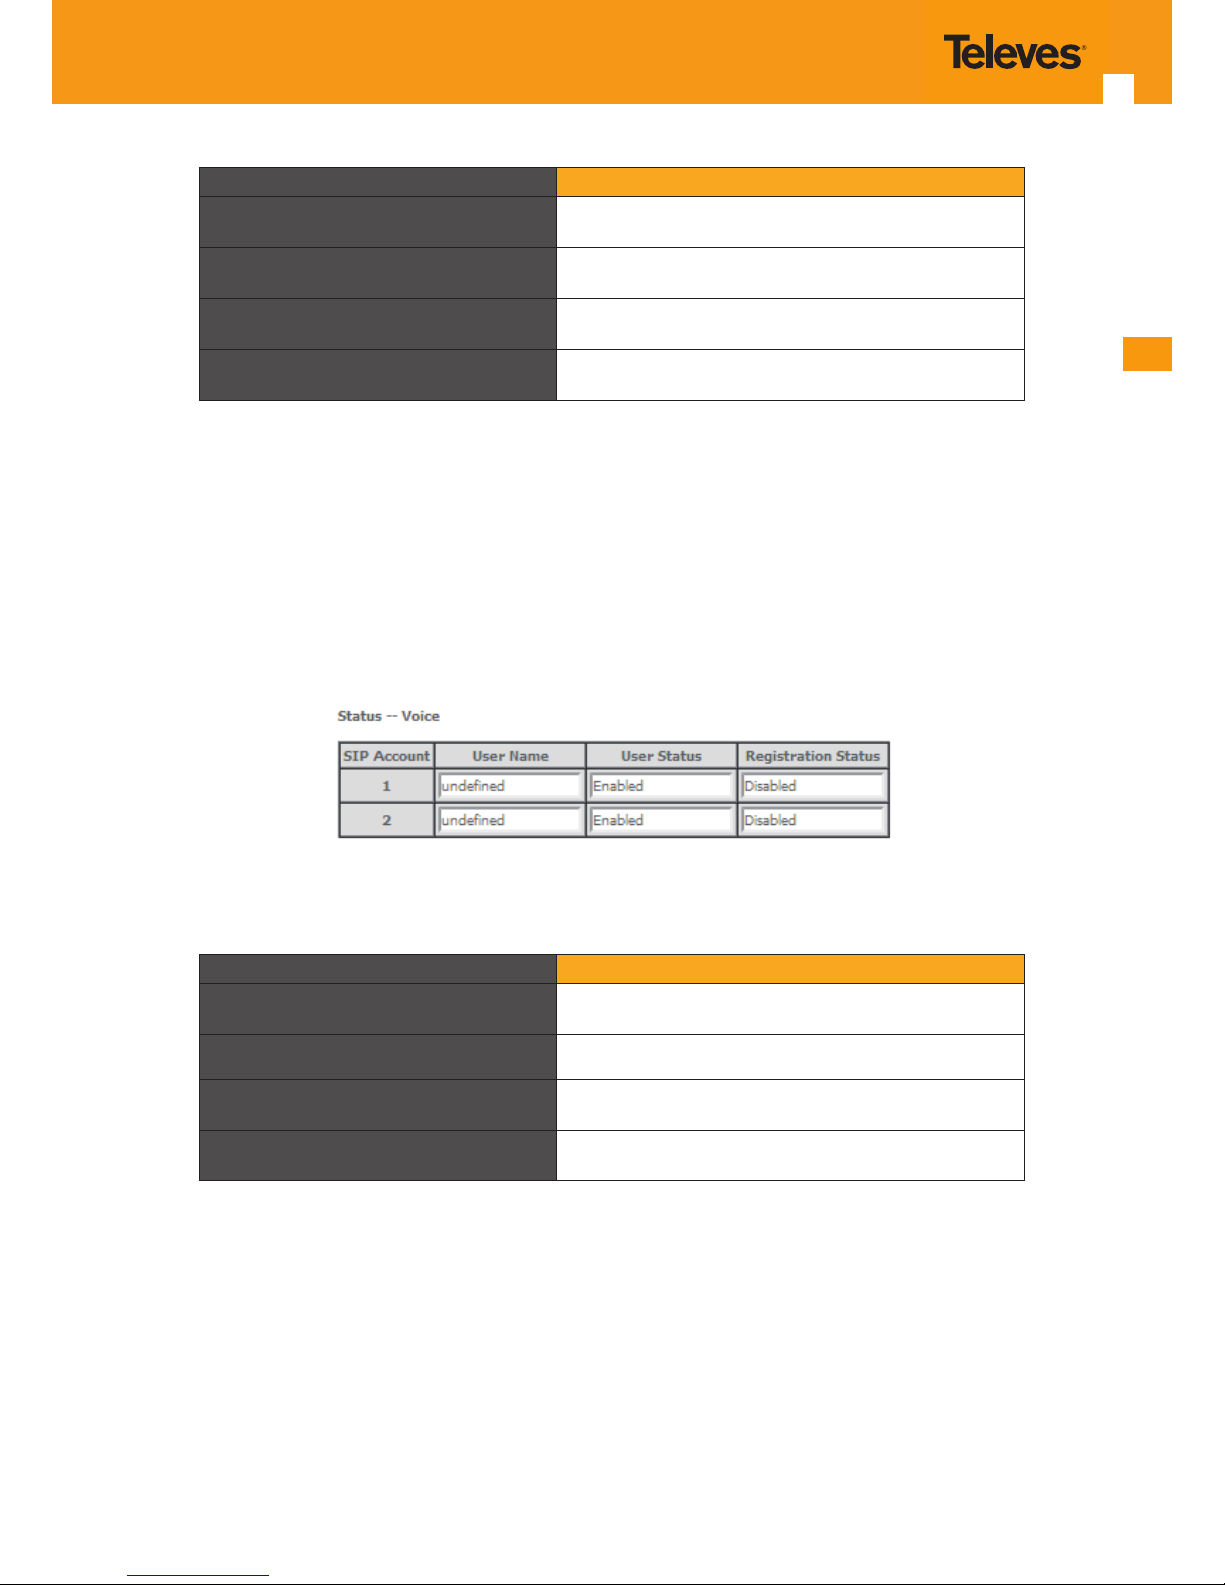
EN
47
Parameter Description
Hostname
External Device(with an IP Address was attributed by DHCP
lease by the Refs. 769501-769502) Name
MAC Address
External Device (with an IP Address was attributed by
DHCP lease by the Refs. 769501-769502) MAC Address
IP Address
External Device IP Address attributed by DHCP lease by the
Refs. 769501-769502
Expires in
Remaining validity time of DHCP leased External Device IP
address
Table 5-8: Device DHCP Leases information Table parameters
5.5.7 Voice
Selection of the Device Info sub-menu VOICE item, compresses the open Device Info sub-menu if expanded (eg Statistics) and shows in the main
window the Device Voice Status information, Figure 5-13
Device Voice Status information parameter description can be found in Table 19
Figure 5-13: Device Voice Status information table
Parameter Description
SIP Account
SIP account identier; two SIP account can be congured
at the Refs. 769501-769502:
User Name SIP Account Access Data Information: Username
User Status
SIP Account Access Data Information: User Status (enabled/disabled)e
Registration Status
Information of the status of SIP Account Registration process: (enabled/disabled)
Table 5-9:Device Voice Status information Table parameters
Page 48
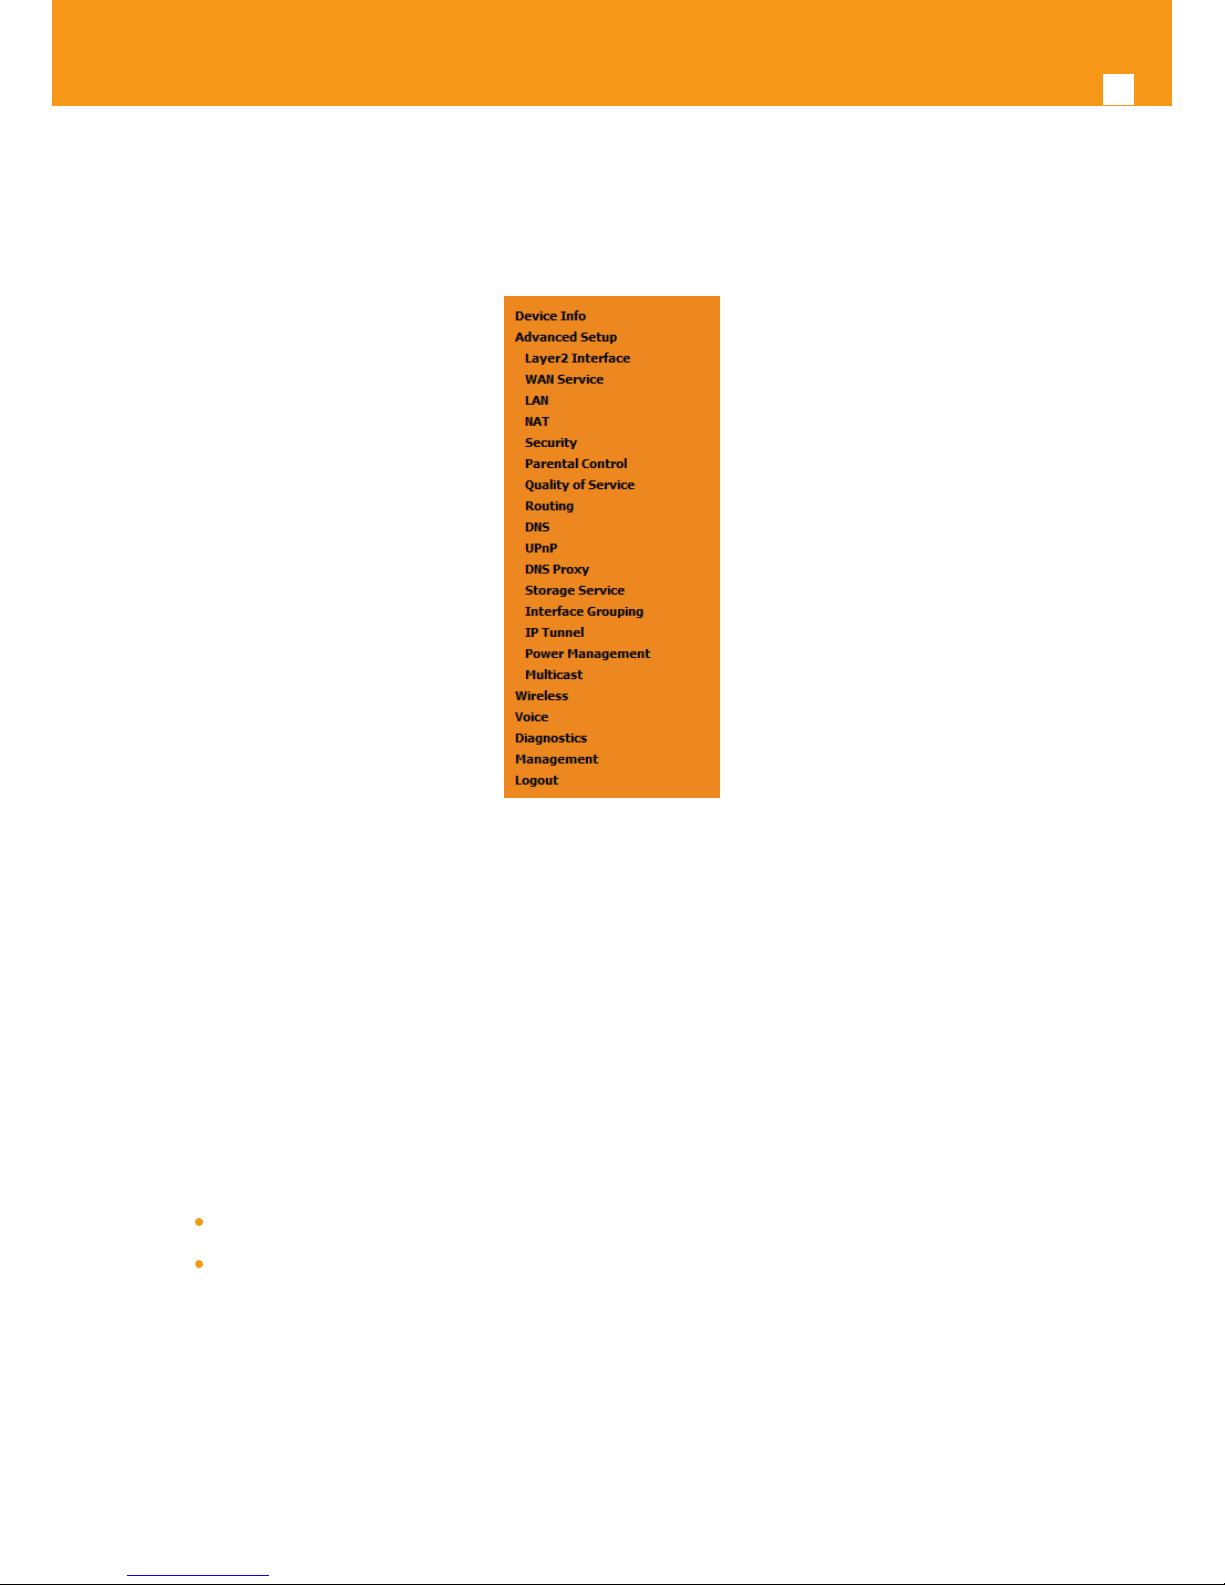
48
GPON ONT
5.6 Advanced Setup
Selection of the main menu item Advanced Setup expands Advanced Setup sub-menu, Figure 5-14.
Figure 5-14: Advanced Setup Expanded Menu
The main Windows shows the Layer2 interface menu, GPON interface conguration window.
5.6.1 Layer2 Interface
This menu item allows the conguration of the wan ONT-wan interface (uplink interface) as GPON wan interface or ETH wan interface (physical
electrical ETH interface). In the last case th
e Refs. 769501-769502 is congured simply as a conventional RGW.
Selection of Advanced Setup sub-menu item Layer2 Interface expands Layer2 Interface submenu items than allow the conguration of the WAN
interface (uplink interface):
GPON Interface
Ethernet Interface
5.6.1.1 GPON Interface
Selection of Advanced Setup, Layer2 Interface sub-menu item GPON interface displays in the main window GPON WAN Interface Conguration
window which is the default conguration for WAN interface, Figure 5-15. In this window it is possible to add or remove GPON WAN interface.
Device DHCP information parameter description can be found in Table 5-10.
Page 49
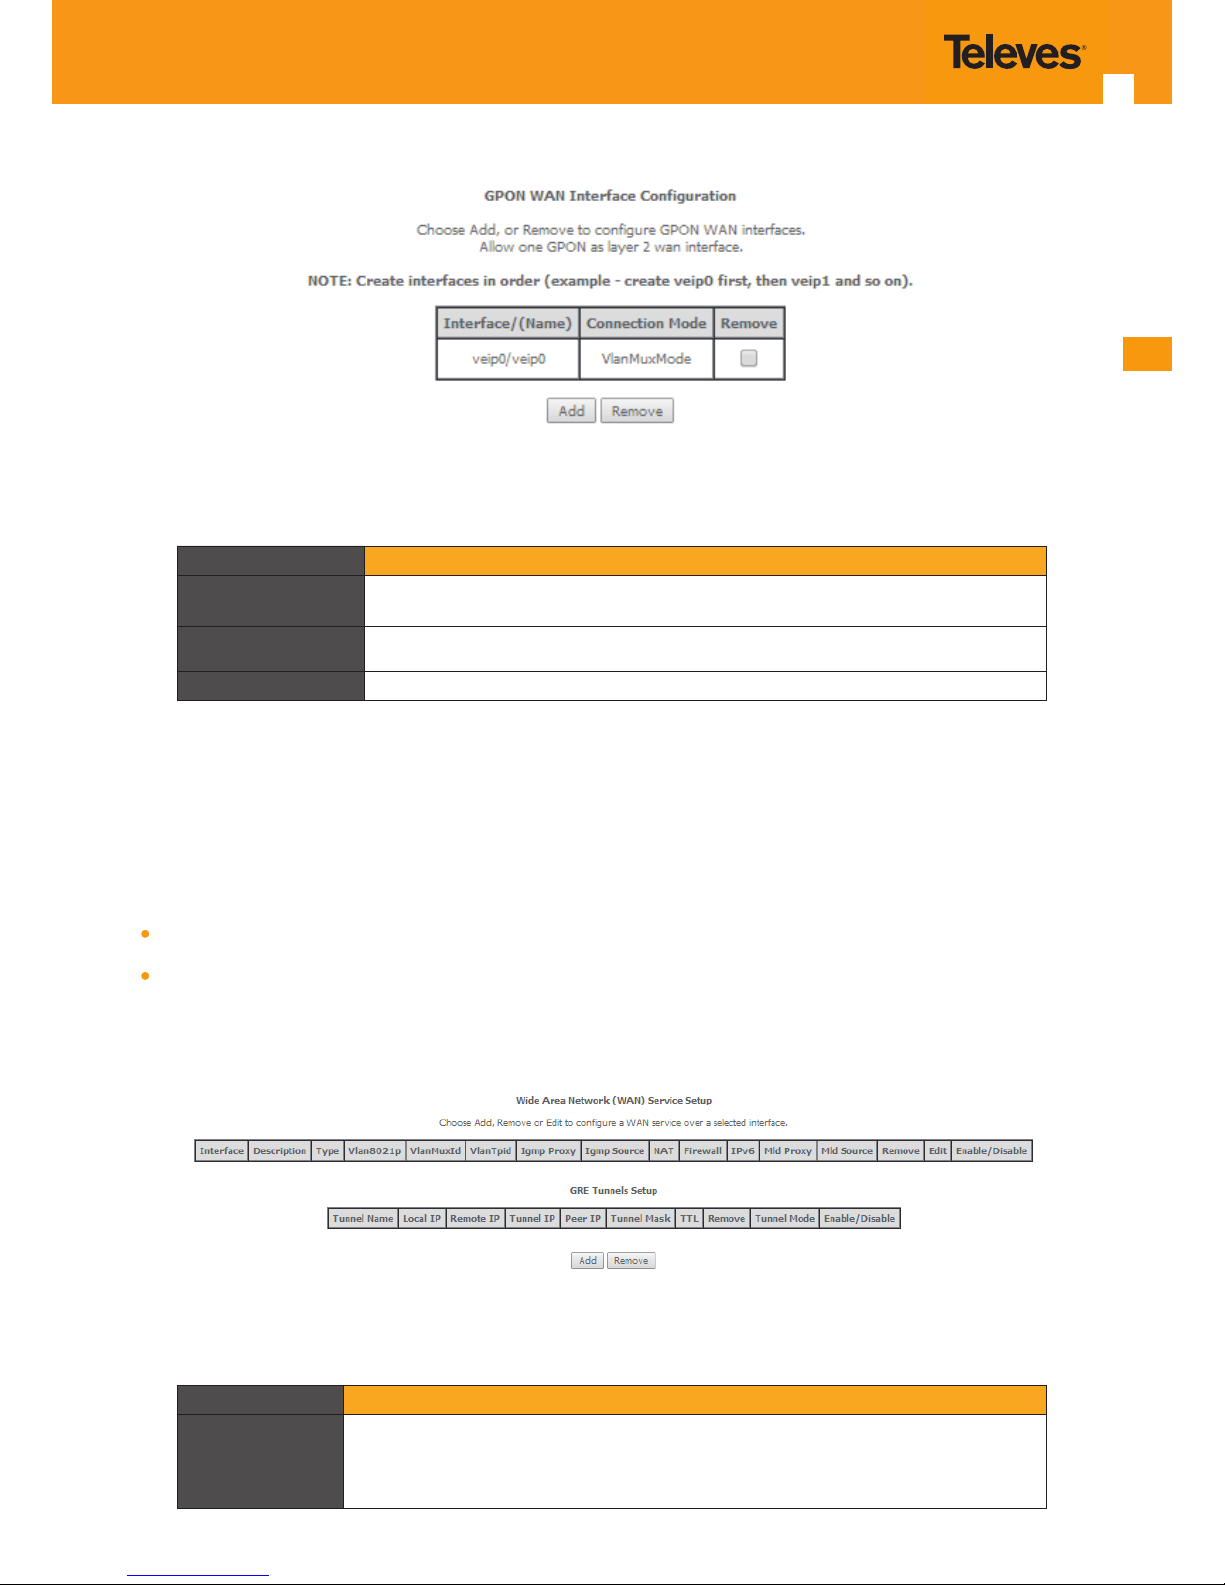
EN
49
Figure 5-15: GPON WAN Interface Conguration- initial window
Parameter Description
Interface/(Name)
Refs. 769501-769502 WAN interface Identication. In the case of GPON Wan interface
– veip0/veip0
Connection Mode Value: VlanMuxMode
Remove If selected, the WAN interface can be removed with Remove button
Table 5-10: GPON WAN interface conguration Table parameters
5.6.2 WAN Service
Selection of Advanced Setup submenu item Wan Service will display in the main window two conguration tables, Figure 5-20:
Wan service setup
GRE tunnels setup
Table parameters’ description can be found in tables Table 5-12 and Table 5-13.
In this window it is possible the Addition and Removal of WAN services.
Figure 5-20: Advanced Setup WAN Service main window
Parameter Description
Interface
WAN interface identication (string); attributed on the Wan interface conguration; if
not set by the user, the system names the interface automatically as “xxx0.n/”, where
xxx is the type of interface (eg ppp stands for pppoe) n is number indicating order of
interface creation, starting in 1
Page 50
50
GPON ONT
Parameter Description
Description
WAN service description; String that can be entered by the user; default values indicates
type of WAN service (pppoe/ipoe/gre/br), used layer 2 interface (eg. veip0/eth1) interface and used vlan id (eg. 11)
Type Identies Wan service Type (PPPoE/IPoE/gre/br)
Vlan8021p
IEEE 802.1P Priority value (0 to 7)- to use for tagged services
Set to “-1” for Untagged services
VlanMuxId Used 802.1Q VLAN ID (0-4094) for tagged services; for untagged services use value “-1”
Vlan Tpid VLAN Tag Protocol Identier;
Igmp Proxy
Flag (enable/disable) ; indicates if IGMP proxy is enabled; to use for multicast congura-
tion in the case of IPv4.
Igmp Source
Flag (enable/disable); indicates if IGMP source is enabled; to use for multicast congura-
tion in the case of IPv4.
Igmp Src Enbl
Flag (enable/disable); indicates if IGMP source is enabled; to use for multicast congura-
tion in the case of IPv4.
NAT Flag (enable/disable); Indicates if NAT is enabled
Firewall Flag (enable/disable); Indicates if Firewall is enabled
IPv6 Flag (enable/disable) ; indicates if IPv6 is enabled
MLD Pxy
Flag (enable/disable) ; indicates if MLD proxy is enabled; to use for multicast congura-
tion in the case of IPv6.
MLD Src
Flag (enable/disable) ; indicates if MLD source is enabled; to use for multicast congura-
tion in the case of IPv6.
Remove If selected, the WAN Service can be removed with Remove button
Edit Flag (enable/disable) ; indicates if IPv6 is enabled
Enable/Disable Flag (enable/disable); indicate if the interface is administratively enabled
Table 5-12: WAN Service Setup Table parameters
Parameter Description
Tunnel Name GRE Tunnel identication (string) congured when gre tunnel is created
Local IP IP address of the local end interface of the GRE tunnel
Remote IP IP address of the local end interface of the GRE tunnel
Tunnel IP Tunnel IP Address
Peer IP Peer IP Address
Tunnel Mask Tunnel mask
TTL Time To Live in seconds
Remove If selected, the GRE Tunnel can be removed with Remove button
Tunnel Mode Indicates if this is a Layer 2 mode tunnel
Enable/Disable Flag (enable/disable); indicate the Tunnel is administratively enabled
Table 5-13: GRE Tunnels Setup Table parameters
5.6.2.1 WAN Service Creation
To create a WAN service, use the ADD button in the Advanced Setup WAN service Main window, Figure 5-20. A new window will be displayed
where is possible to select on a combo box the
Refs. 769501-769502 WAN interface associated to the service to create, Figure 5-21. Once
selected the WAN interface use the Next Button, Figure 5-22, to progress to the next WAN service conguration window – Type of service
selection and service conguration, Figure 5-23.
Page 51
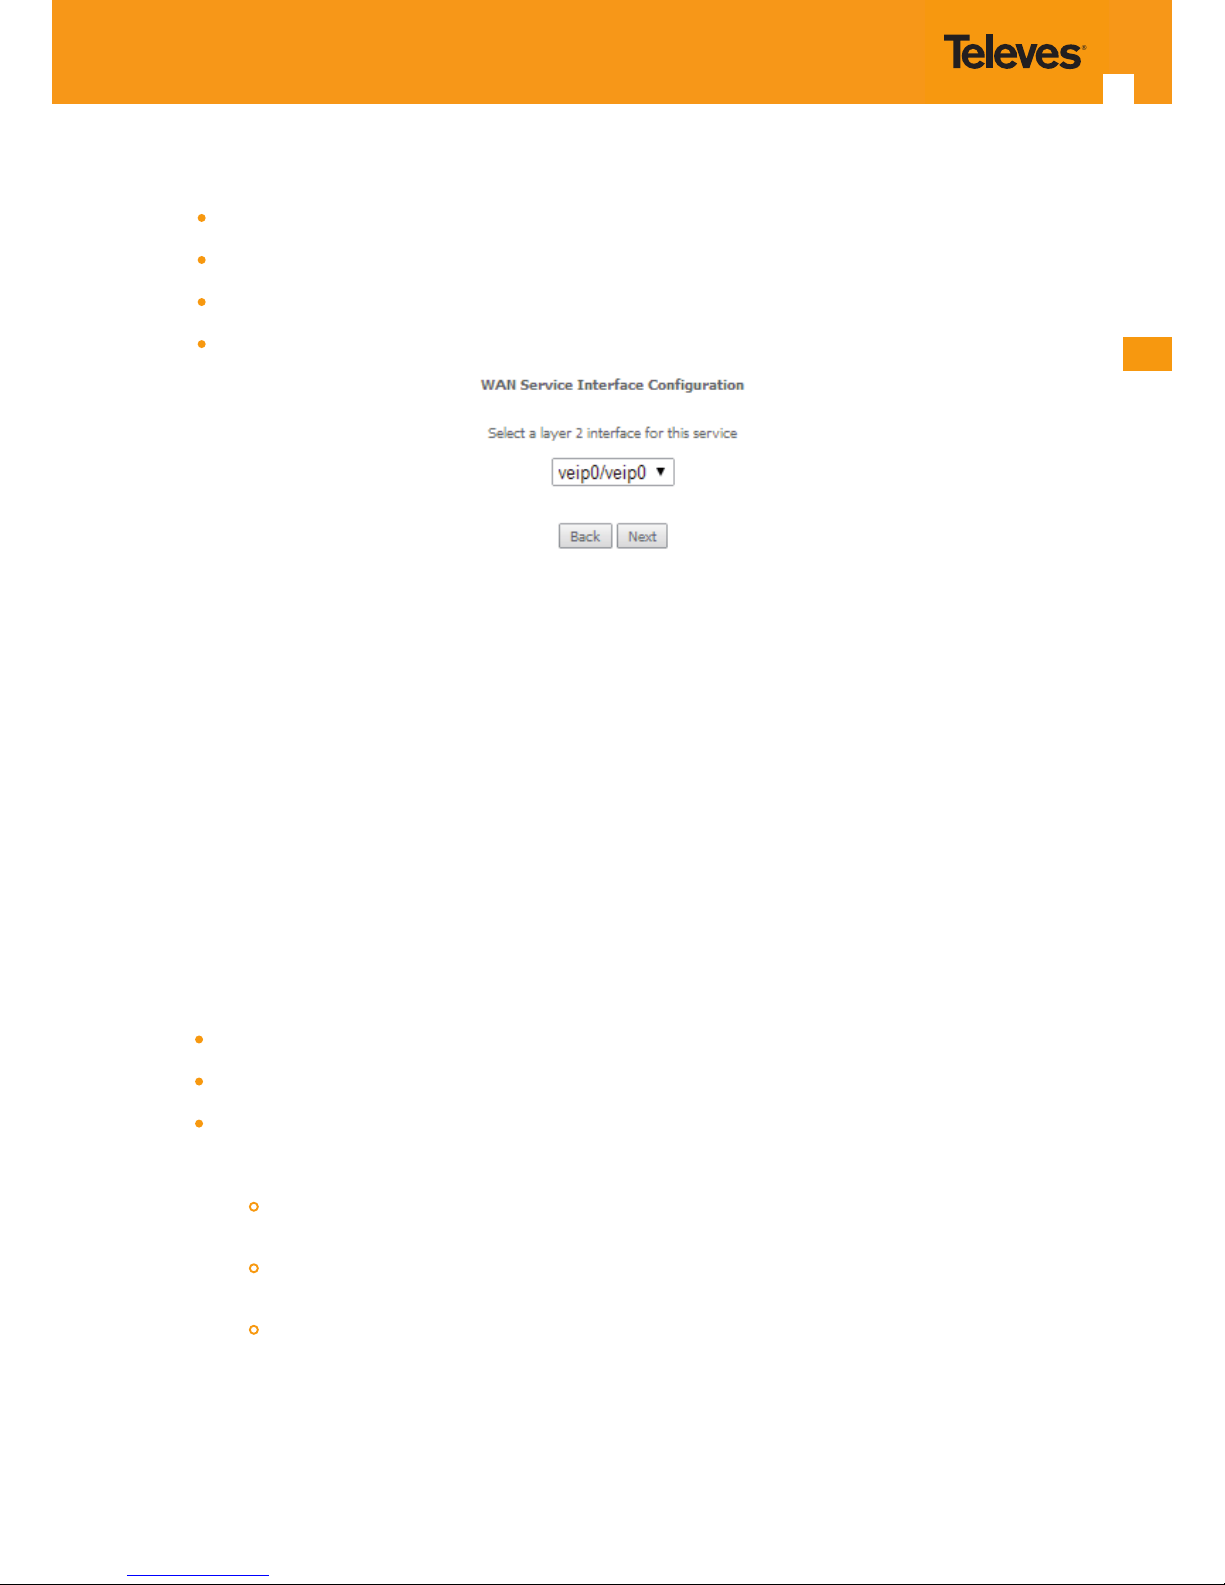
EN
51
Four types of WAN services can be created and congured:
PPP over Ethernet (PPPoE)
IP over Ethernet (IPoE)
GRE Tunneling (over Layer 2)
Bridging.
Figure 5-22: WAN service Interface selection for the WAN service to setup
5.6.2.1.1 PPPoE Type of Service Creation
After the selection of the WAN interface associated to the service to create, Figure 5-21 and Figure 5-22, use the Next button Figure 5-22, to progress to the next WAN Service setup window- Wan service Conguration, Figure 5-23
At this window execute the following steps:
STEP 1. Select the PPP over Ethernet (PPPoE) WAN service type.
STEP 2. At the Field Service Description enter a string for the service description; the default service description is a string automatically
lled in when the type o device is selected(Step1) and composed by the type of Service followed by underscore and the WAN interface name , e.g. pppoe_veip0
Next elds of the WAN service conguration are related to VLAN tagging conguration:
802.1P priority; denition of the upstream trac classication by attributing a Pbit value (0->7; 0 being the lowest priority trac)
802.1Q VLAN ID, Species the VLAN identier; values from 0 to 4096
VLAN TPID; Tag Protocol Identier (TPID) is a 16-bit eld of the IEEE 802.1Q header, that is used to identify the frame as a tagged frame;
Possible values are:
0x8100, TPID default value; Used for single tagged frames or for double tagged frames as the inner or customer VLAN tag
(802.1ad conventions)
0x88A8, Used in double tagged frames, for the outer or service VLAN tag (802.1ad conventions); in this case the inner VLAN
(C-VLAN) tag TPID has the default value of 0x8100;
0x9100, Used in double tagged frames, for the outer or service VLAN tag (older version of 802.1Q); in this case the inner
VLAN (C-VLAN) tag TPID has the default value of 0x8100;
Page 52
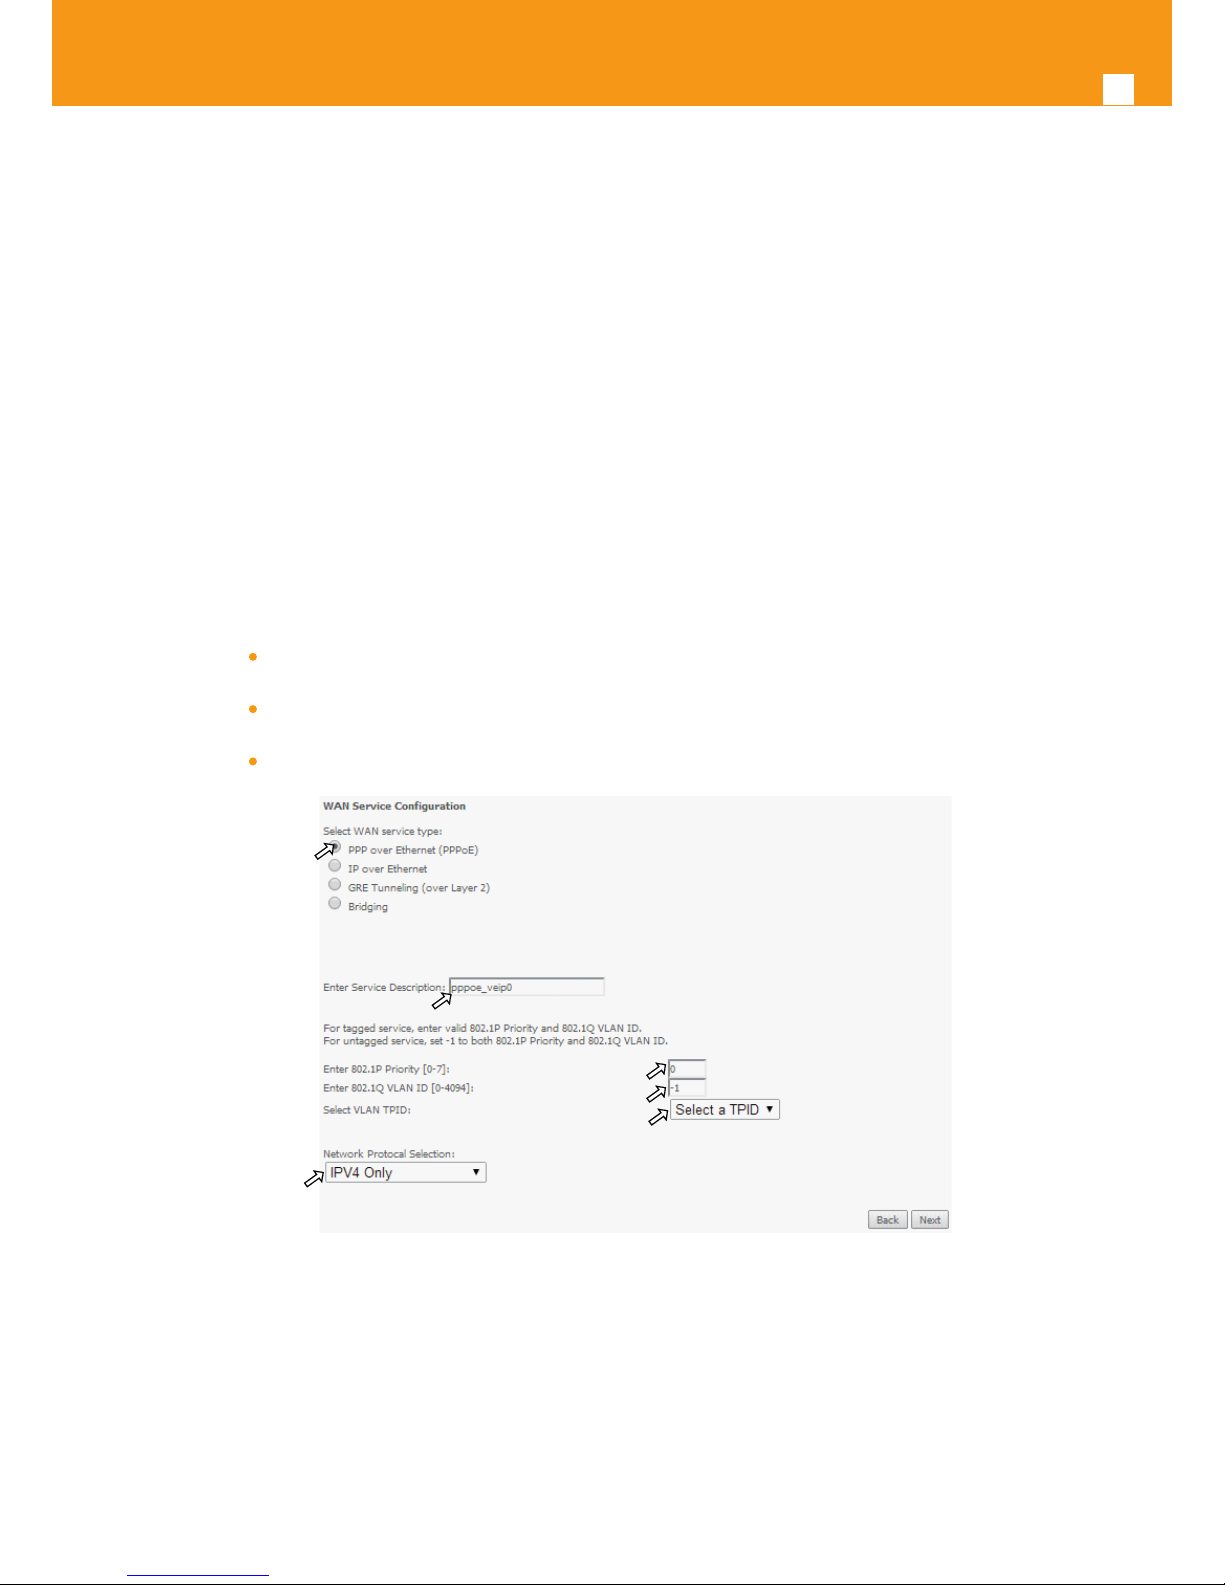
52
GPON ONT
5.6.2.1.2 VLAN Tagging Conguration Procedure
STEP 3. For tagged service, at the eld 802.1P priority, enter the pbit value (0-7) to mark the upstream trac according to the desired CoS
for the service to create; a higher value corresponds to a higher priority CoS; For untagged service leave the led with the default
value of -1;
STEP 4. For tagged service, at the VLAN ID eld enter the VLAN ID value (0-4094) of the VLAN used by the service.
For untagged service leave the eld with the default value of -1;
STEP 5 For tagged service select a TPID value from the selection combo box, Figure 5-23.
0x8100, TPID default value; if selected a single tagged service is congured.
0x88A8 or 0x9100, TPID used for the outer VLAN (S-VLAN) for double tagged services; if selected a double VLAN tagged service is
congured; in this case the inner VLAN (C-VLAN) tag TPID has the default value of 0x8100;
STEP 6 At the eld Network Protocol Selection use the selection combo box to choose one of the available options:
IPv4 Only (default value);
IPv4 & IPv6 (Dual Stack);
IPv6 Only;
1
2
3
4
5
6
Figure 5-23: WAN service setup – type of service selection and service conguration – PPPoE service
STEP 7. Once the WAN service setup parameters are congure use Next button, Figure 5-26, to progress to the next WAN Service setup
window- Connection establishment parameters conguration, Figure 5-27
Page 53
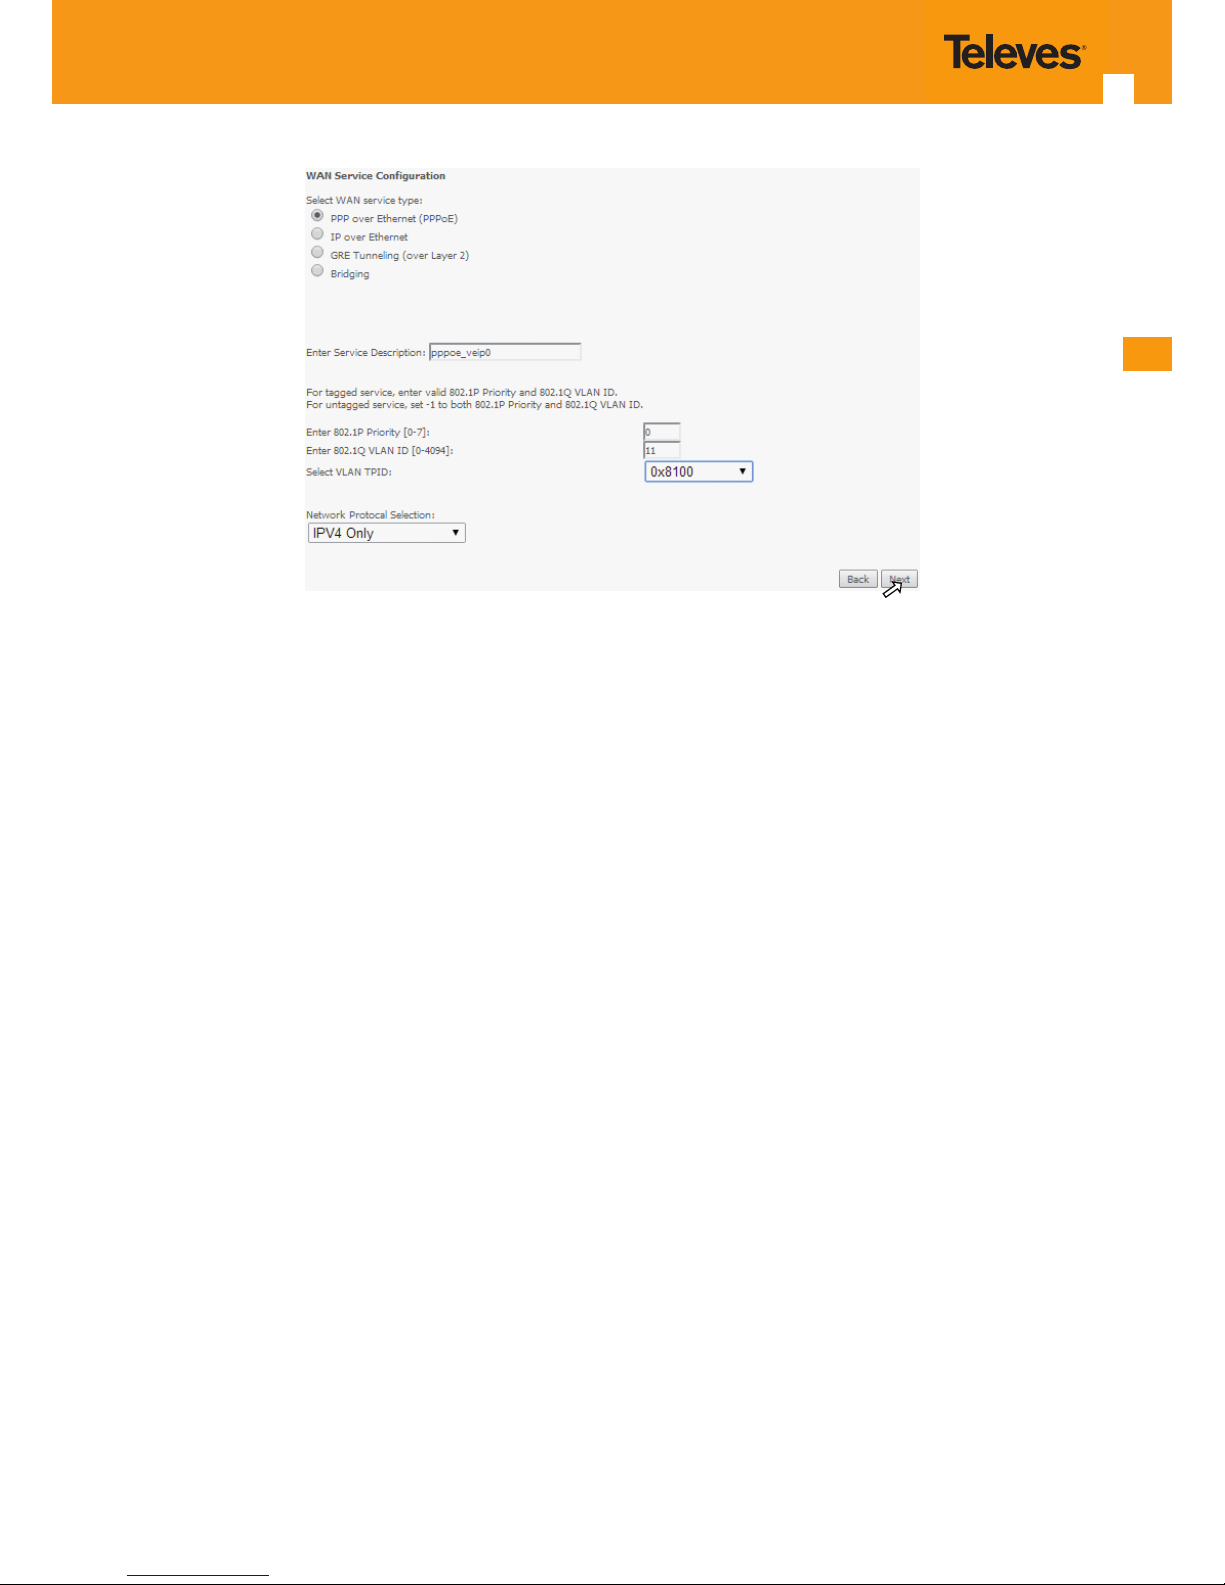
EN
53
7
Figure 5-26: WAN service setup– type of service selection and service conguration – nalize type of service conguration
Page 54
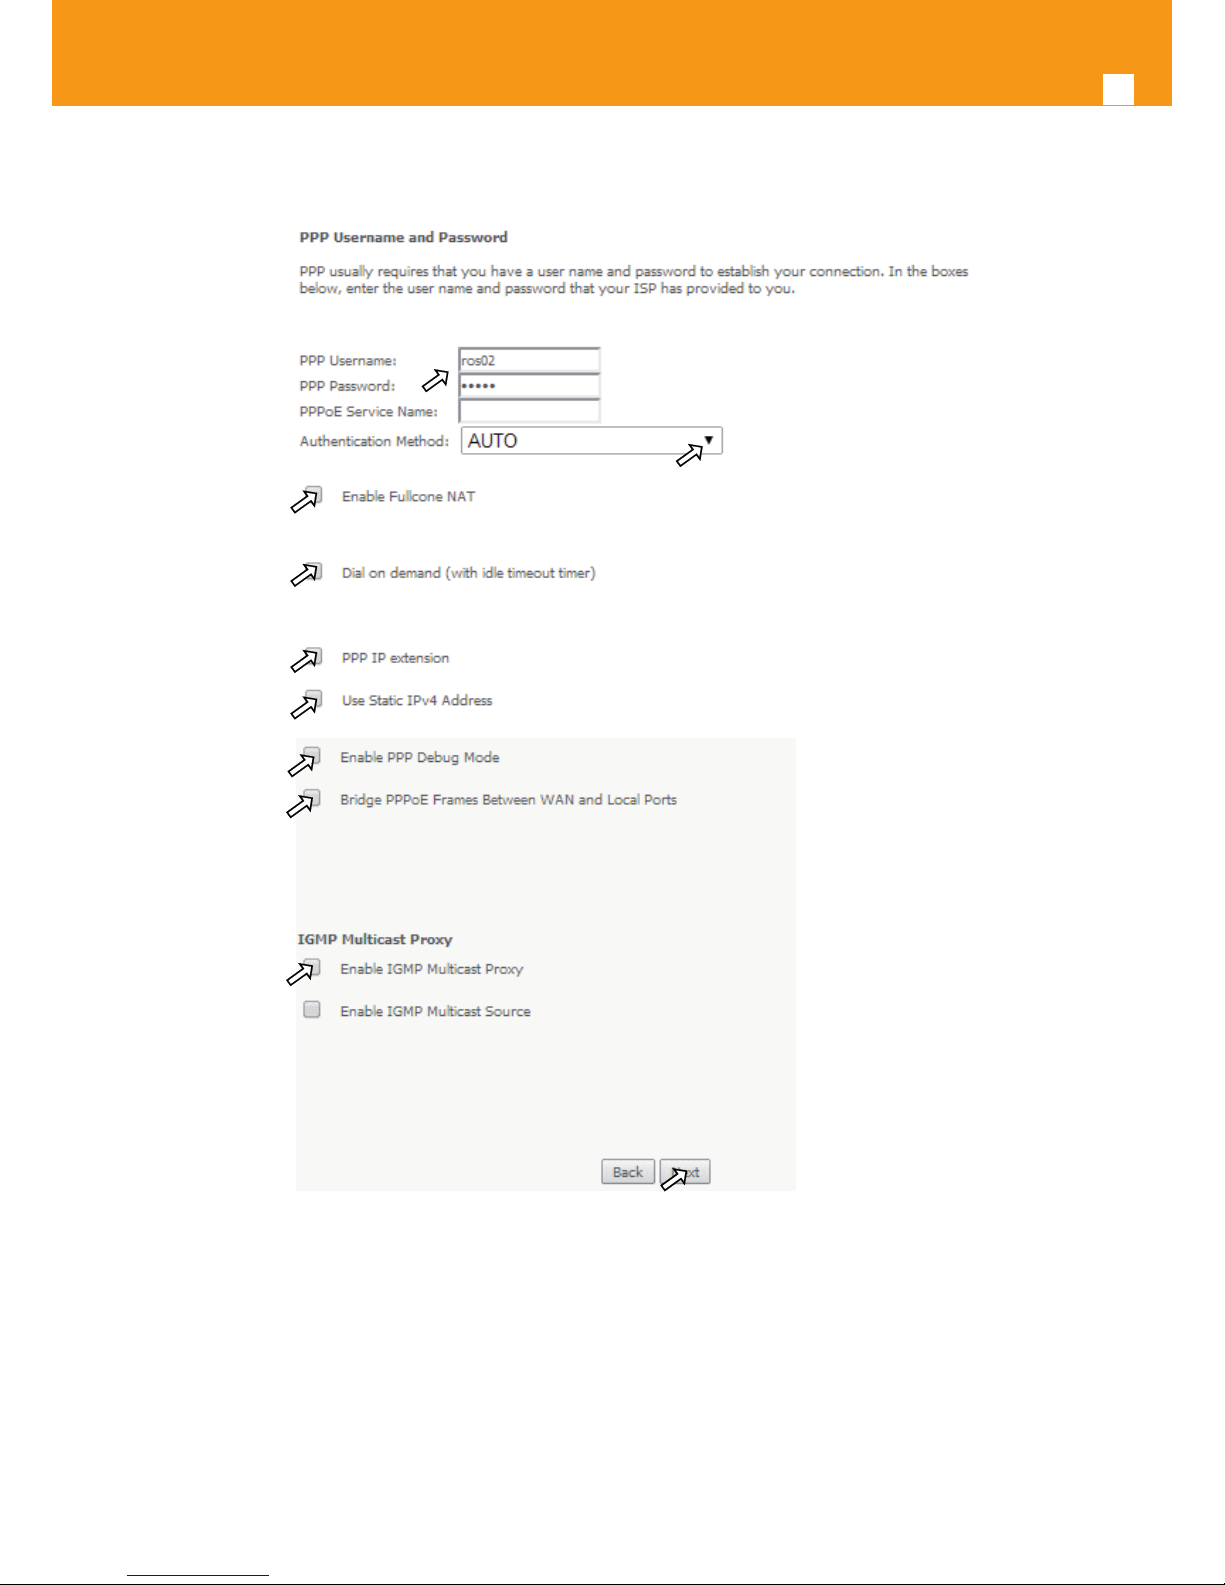
54
GPON ONT
The WAN Service Setup window– Connection establishment conguration, Figure 5-27, allows the conguration of the PPoE connection establishment parameters, as explained bellow.
4
2
3
1
5
6
7
9
8
10
Figure 5-27: WAN Service Setup – Connection establishment conguration window
Page 55
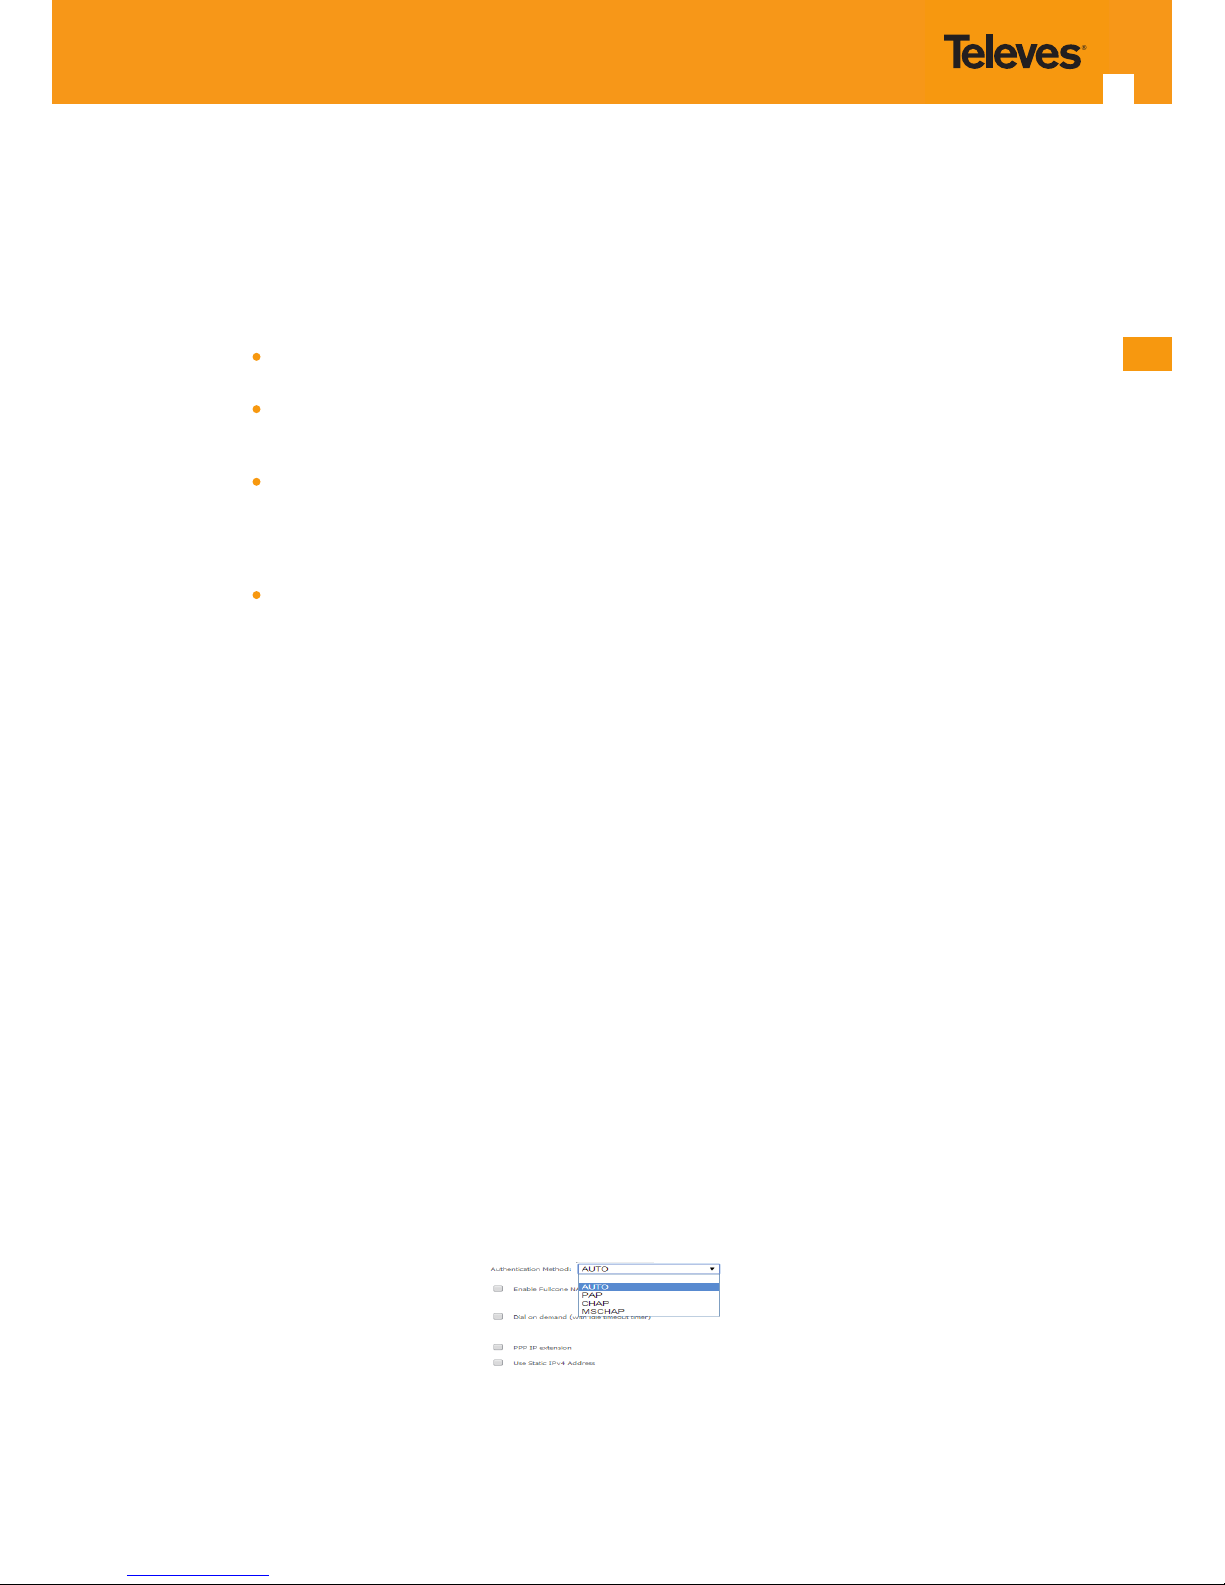
EN
55
5.6.2.1.3 PPPoE Connection Establishment Parameters Conguration
STEP 1. Select the PPP username and password and use the access data provided by your ISP Username and password) to establish the
PPPoE connection, Figure 5-27;
STEP 2. At the authentication method selection combo box select one of the available option, Figure 5-28:
AUTO;
PAP, Password Authentication Protocol, simple unsecure method of authentication since password are send unencrypted
over the network; the authentication is done once upon link establishment.
CHAP, Challenge-Handshake Authentication Protocol, secure authentication method, uses a secret known by the client
and the authentication server; the authenticator sends a challenge to which the client must answer to by using the
secret. The answer is compared against the result obtained by the authenticator itself using the secret. CHAP periodically
veries the identity of the client by sending a new challenge.
MSCHAP, Microsoft extension to the CHAP protocol – is a modied CHAP.
STEP 3. If Fullcone NAT is to be used select the option Enable Fullcone NAT; If enabled a warning message on the disadvantages of its use
is shown, Figure 5-29
FullCone NAT is also known as one-to-one NAT: An LAN internal address, port pair is mapped to an external address, port pair so
that any packets from the internal address, port pair will be sent through the external address, port pair and any external host can
send packets to the internal Address, Port pair by sending packets to external Address, Port pair. Once established a fullcone NAT
mapping for LAN internal address and port, it can be reached by any external host without the need of any request from the LAN
internal address.
STEP 4. If Dial on Demand is selected inactivity timeout period in minutes must be specied, Figure 5-30. This corresponds to the time of
inactivity (without trac) after which the PPPoE connection goes down; the connection recovers when activity is detected.
STEP 5. Selected if PPP IP extension is to be used, Figure 5-27
STEP 6. If Use Static IPv4 is selected, the IPv4 address must me entered, Figure 5-31
STEP 7. Selection of Enable PPP debug mode, Figure 5-27, allows to see the packets exchanged in the PPP connection.
STEP 8. Bridge PPPoE Frames between WAN and local ports congures bridging mode
STEP 9. IGMP multicast proxy conguration allows the conguration as either IGMP proxy ort IGMP source and enable/disable Multicast
VLAN lter, Figure 5-32.
STEP 10. Once the Connection establishment parameters are congure use Next button, Figure 5-27, to progress to the next WAN Service
setup - Routing Default Gateway conguration window, Figure 5-33.
Figure 5-28: WAN Service Setup - Connection establishment conguration window- ppp authentication method available options
Page 56
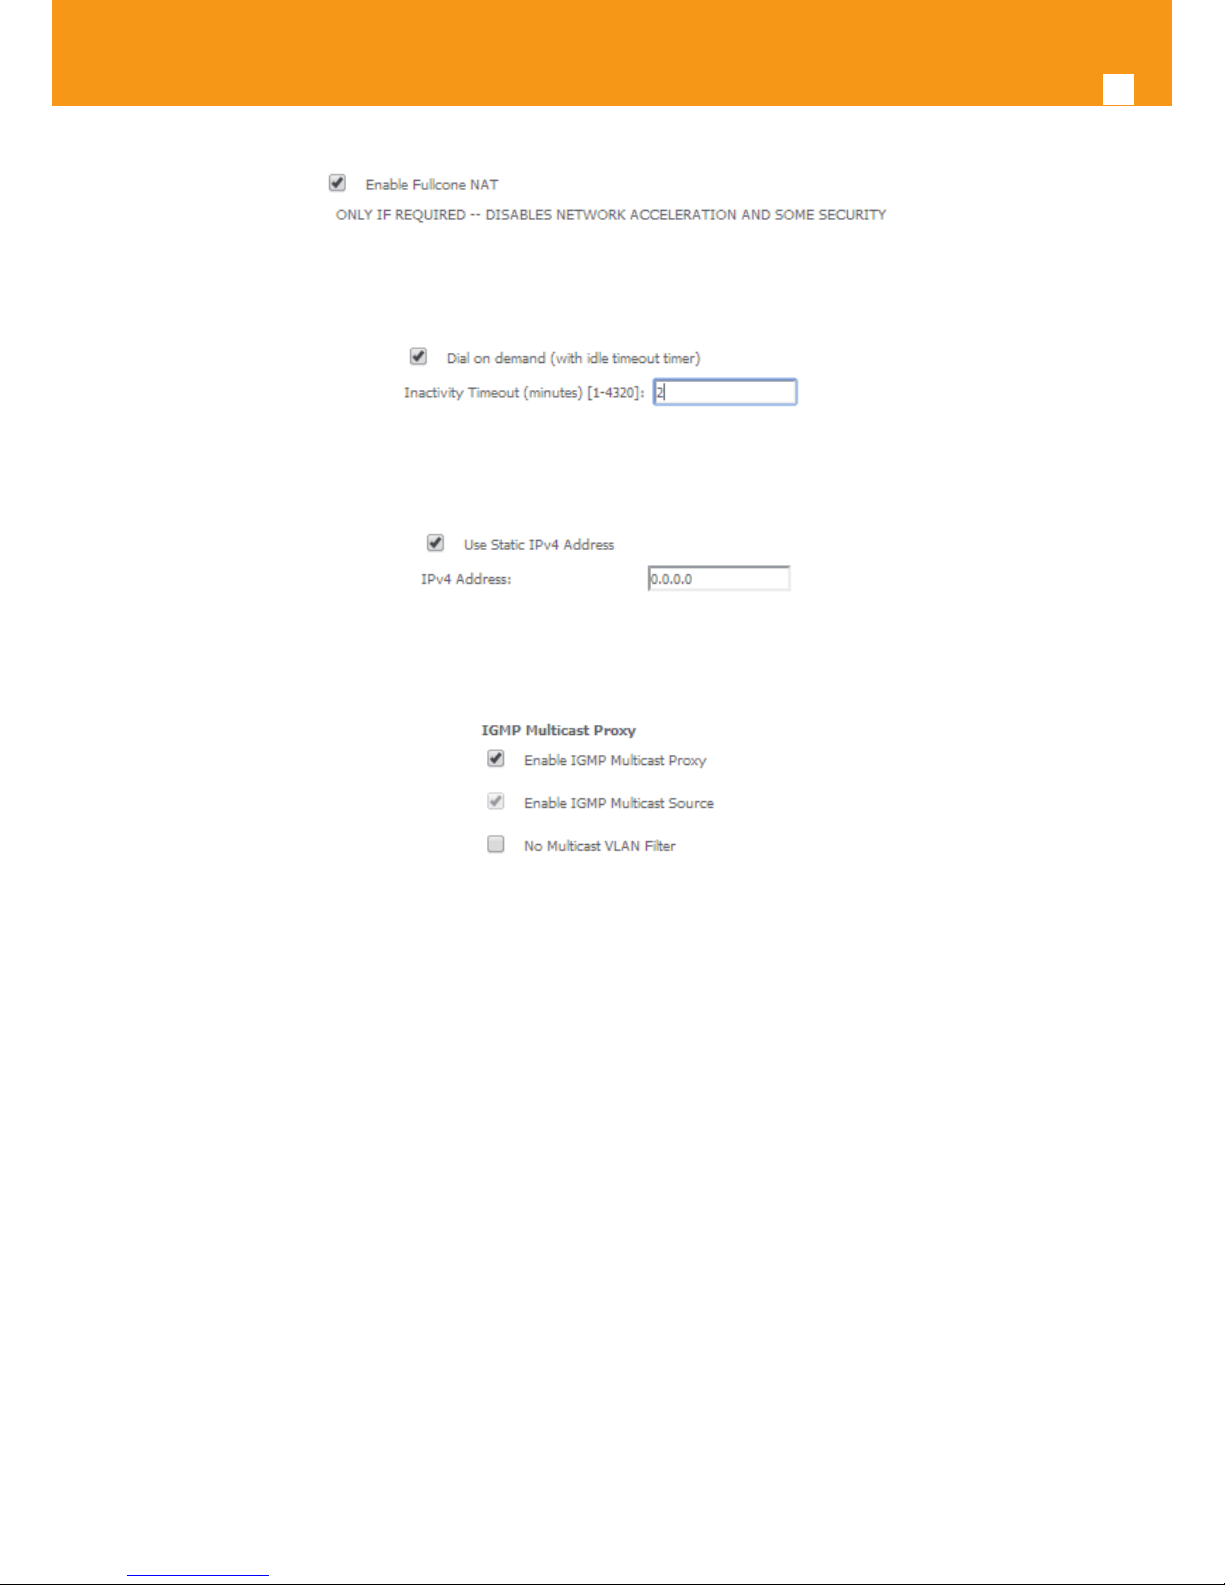
56
GPON ONT
Figure 5-29:WAN Service Setup – Connection establishment conguration window- Enable fullcone NAT warning message
Figure 5-30:WAN Service Setup – Connection establishment conguration window- Dial on demand Conguration
Figure 5-31:WAN Service Setup – Connection establishment conguration window- Use of static IPv4 Conguration
Figure 5-32: WAN Service Setup – Connection establishment conguration window- IGMP Multicast Proxy conguration
5.6.2.1.4 Routing Default Gateway Conguration
The Routing Default Gateway conguration window presents two lists:
• Selected Default Gateway Interfaces: the WAN interfaces that can be used as default gateway interfaces are listed here; only one interface
will be used as default gateway interface- this interface will be the highest priority interface of the connected WAN interfaces in this list;
WAN interface priority is based on its position on the list, the rst one of the list being the highest priority interface.
To change WAN interface priority, its position in the list must be changed; that can be achieved by removing all from the Selected Default Gateway Interfaces list and adding them back in the desired order.
• Available Routed WAN Interfaces: all dened available routed WAN interfaces are listed here; these interfaces can be moved to the Selected Default Gateway interfaces list
If there is only one WAN interface dened in the system, as in the example presented, this will be selected by the system as the default gateway
interface thus being presented is the Selected default gateway list on the left.´
If more WAN interfaces are shown in the list on the right (available routed WAN interfaces) one or more can moved to the list on the left and be
selectable as default gateway routed interface according to its priority in the list.
Page 57
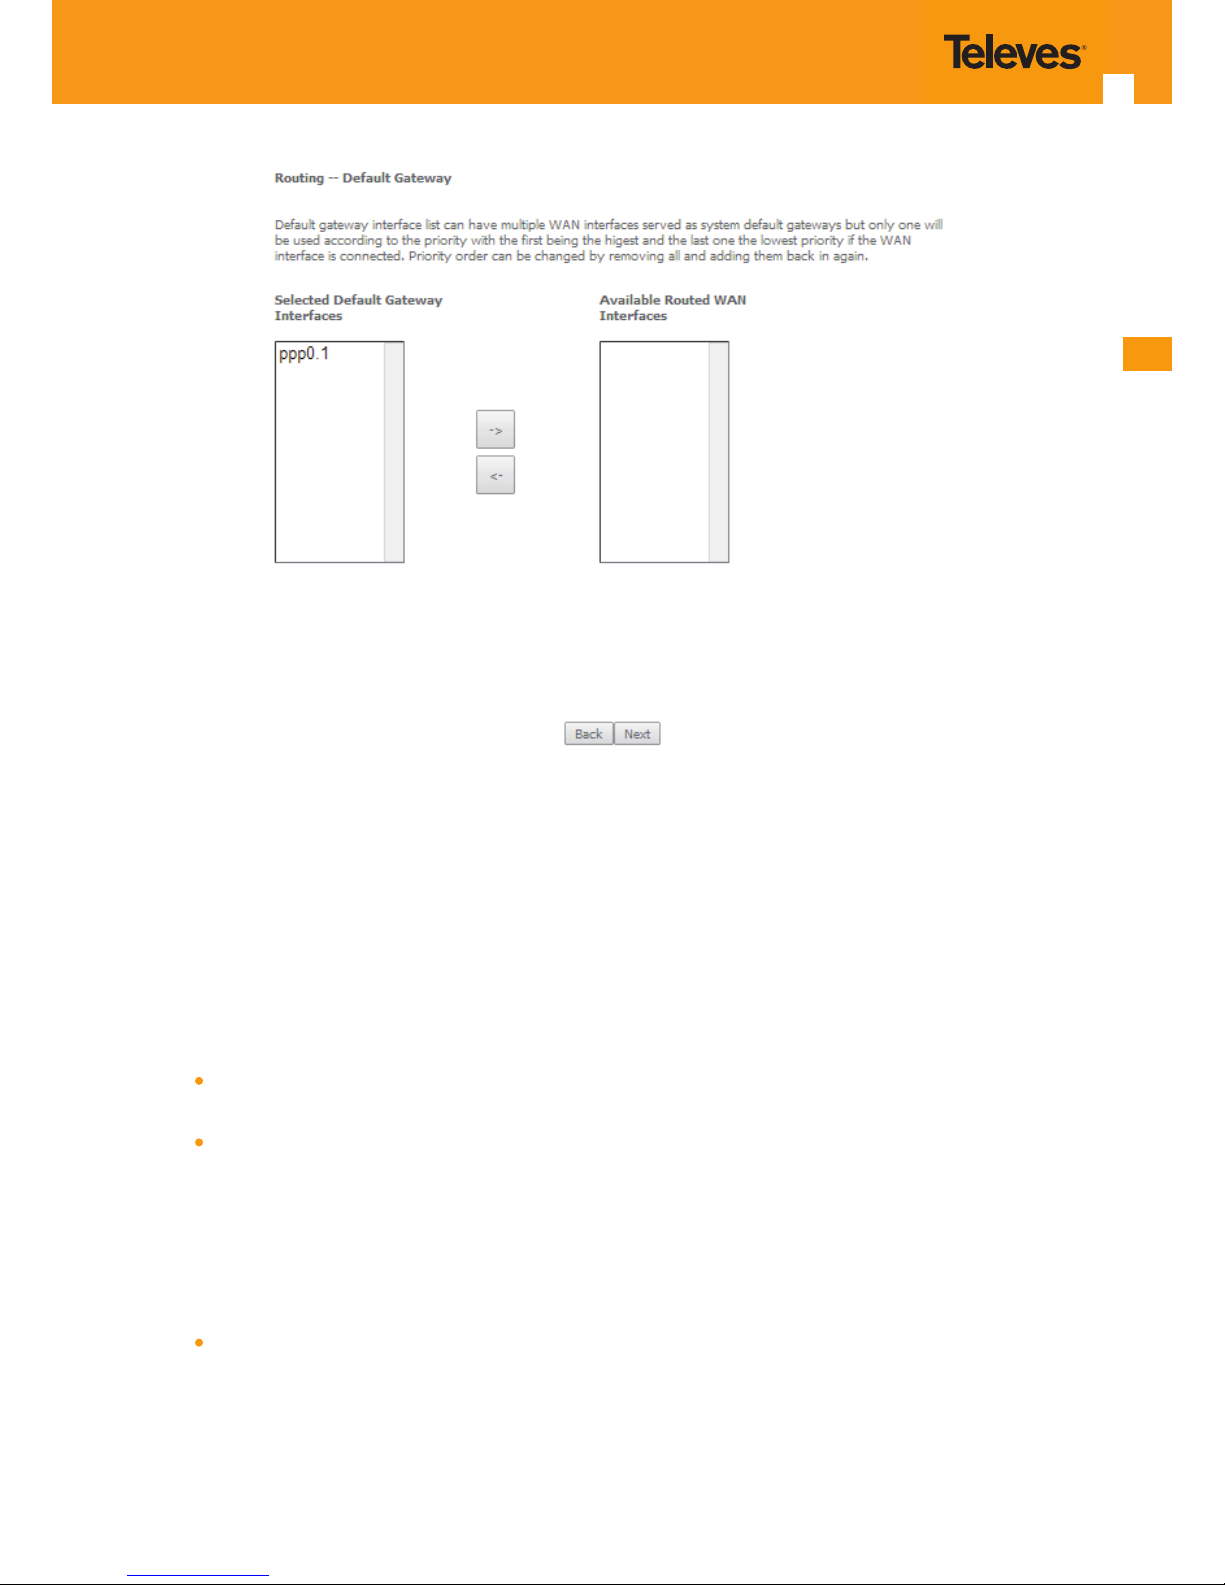
EN
57
Figure 5-33: WAN Service setup - Routing Default Gateway conguration window
After default gateway interface conguration, use the Next button, Figure 5-33, to progress to the next WAN Service setup – DNS Server conguration parameters window, Figure 5-34.
5.6.2.1.5 DNS Server Conguration
DNS server interface can
either be selected from available WAN interfaces, Figure 5-34, 1, from the list Selected DNS Server Interfaces, according to its priority
(please see description bellow),
or use a Static DNS IP address, in which case this option must be selected, Figure 5-34, 2, and the Static DNS servers (primary and
secondary) IP addresses must be entered.
5.6.2.1.5.1 Selection of DNS Server Interfaces from Available WAN Iinterfaces
The DNS Server Conguration window presents two lists:
Selected DNS Server Interfaces: the WAN interfaces that can used as system DNS Server interfaces are listed here; only one interface
will be used as DNS server interface- this interface will be the highest priority interface of the connected WAN interfaces in this list;
WAN interface priority is based on its position on the list, the rst one of the list being the highest priority interface.
To change WAN interface priority, its position in the list must be changed; that can be achieved by removing all from the
Selected DNS Server Interfaces list and adding them back in the desired order.
Page 58
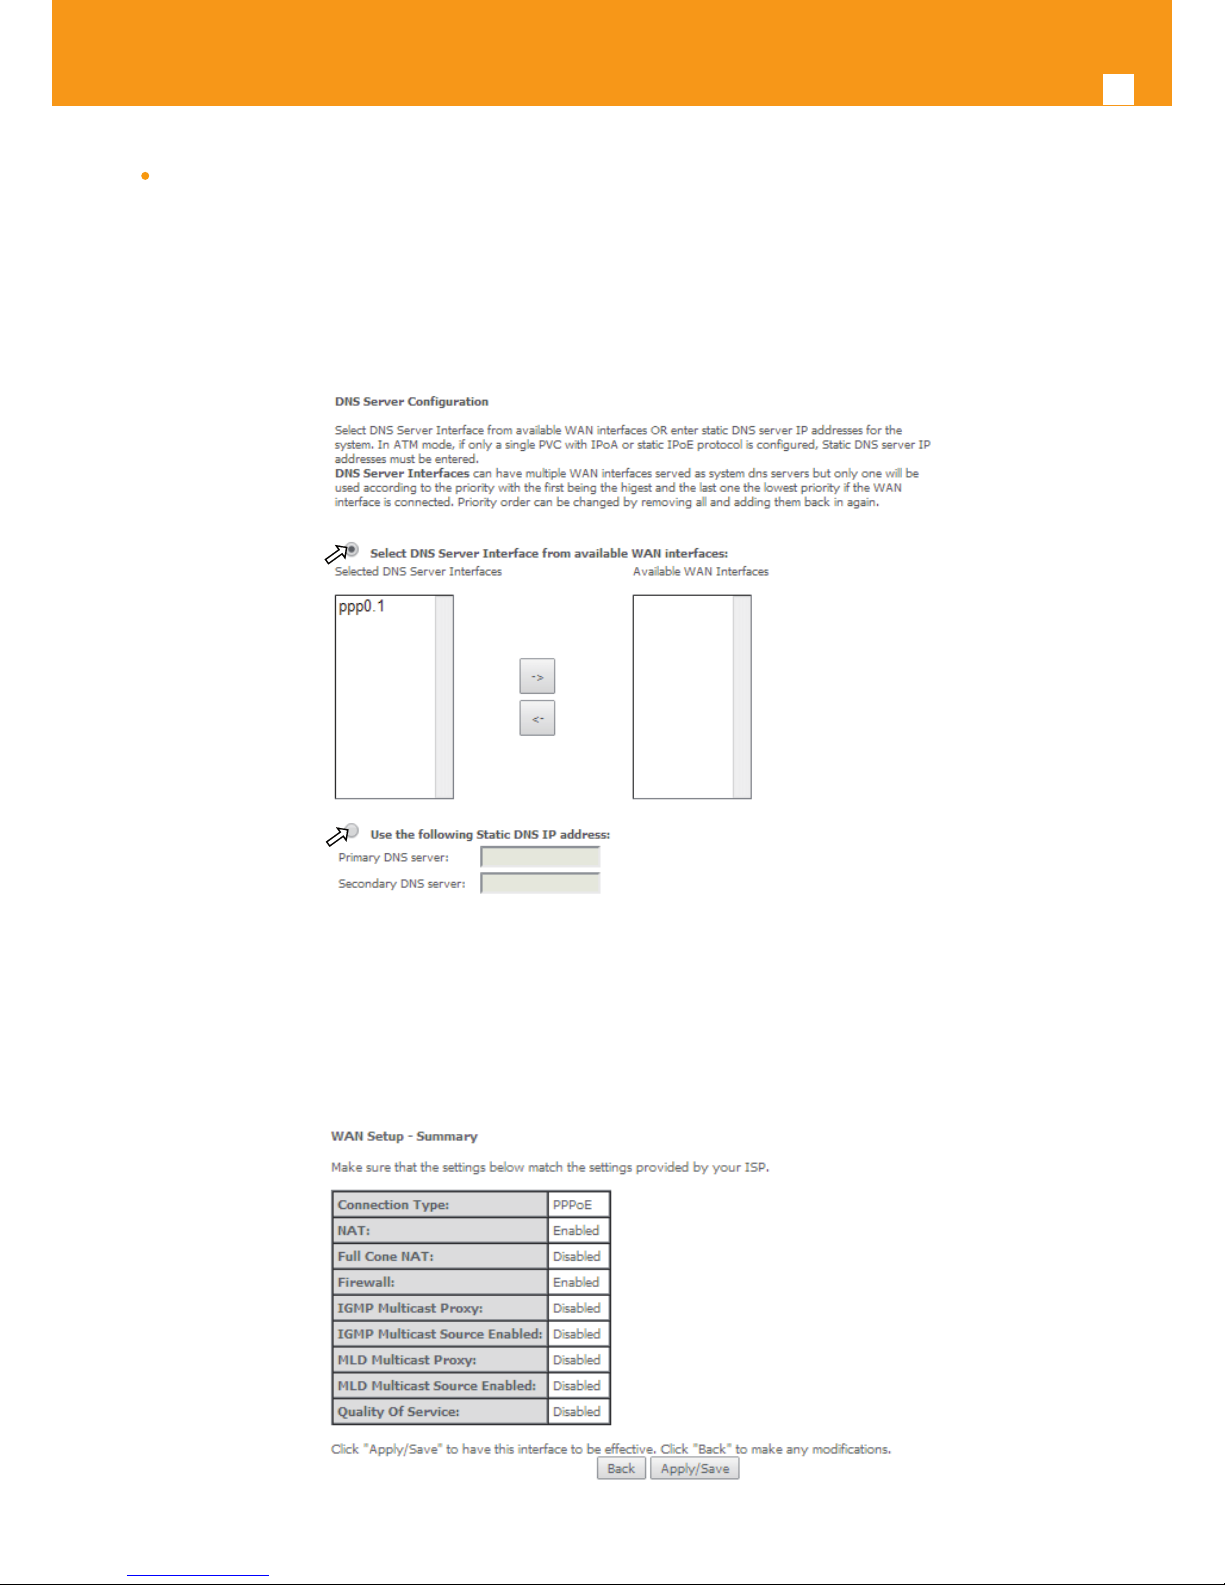
58
GPON ONT
Available WAN Interfaces: all dened available routed WAN interfaces are listed here; these interfaces can be moved to the Selected DNS
Server interfaces list
If there is only one WAN interface dened in the system, as in the example presented, this will be selected by the system as the default
gateway interface thus being presented is the Selected DNS Server list on the left.´
If more WAN interfaces are shown in the list on the right (available WAN interfaces) one or more can moved to the list on the left and be selectable
as Selected DNS Server interface according to its priority in the list.
2
1
Figure 5-34: WAN Service setup – DNS Server conguration window
Once the DNS server conguration is done the PPPoE WAN srvice conguration is complete. Use the Next button to progress to the WAN Service
Setup Summary window, Figure 5-35. This table should reect the conguration for the WAN service setup parameters than have been entered on
the successive WAN service setup conguration windows. Network Address Translation ag and Firewall ag default congurations are enabled.
Please verify the presented conguration match the settings provided by the ISP for this service.
Figure 5-35: WAN Service Setup Summary window
Page 59
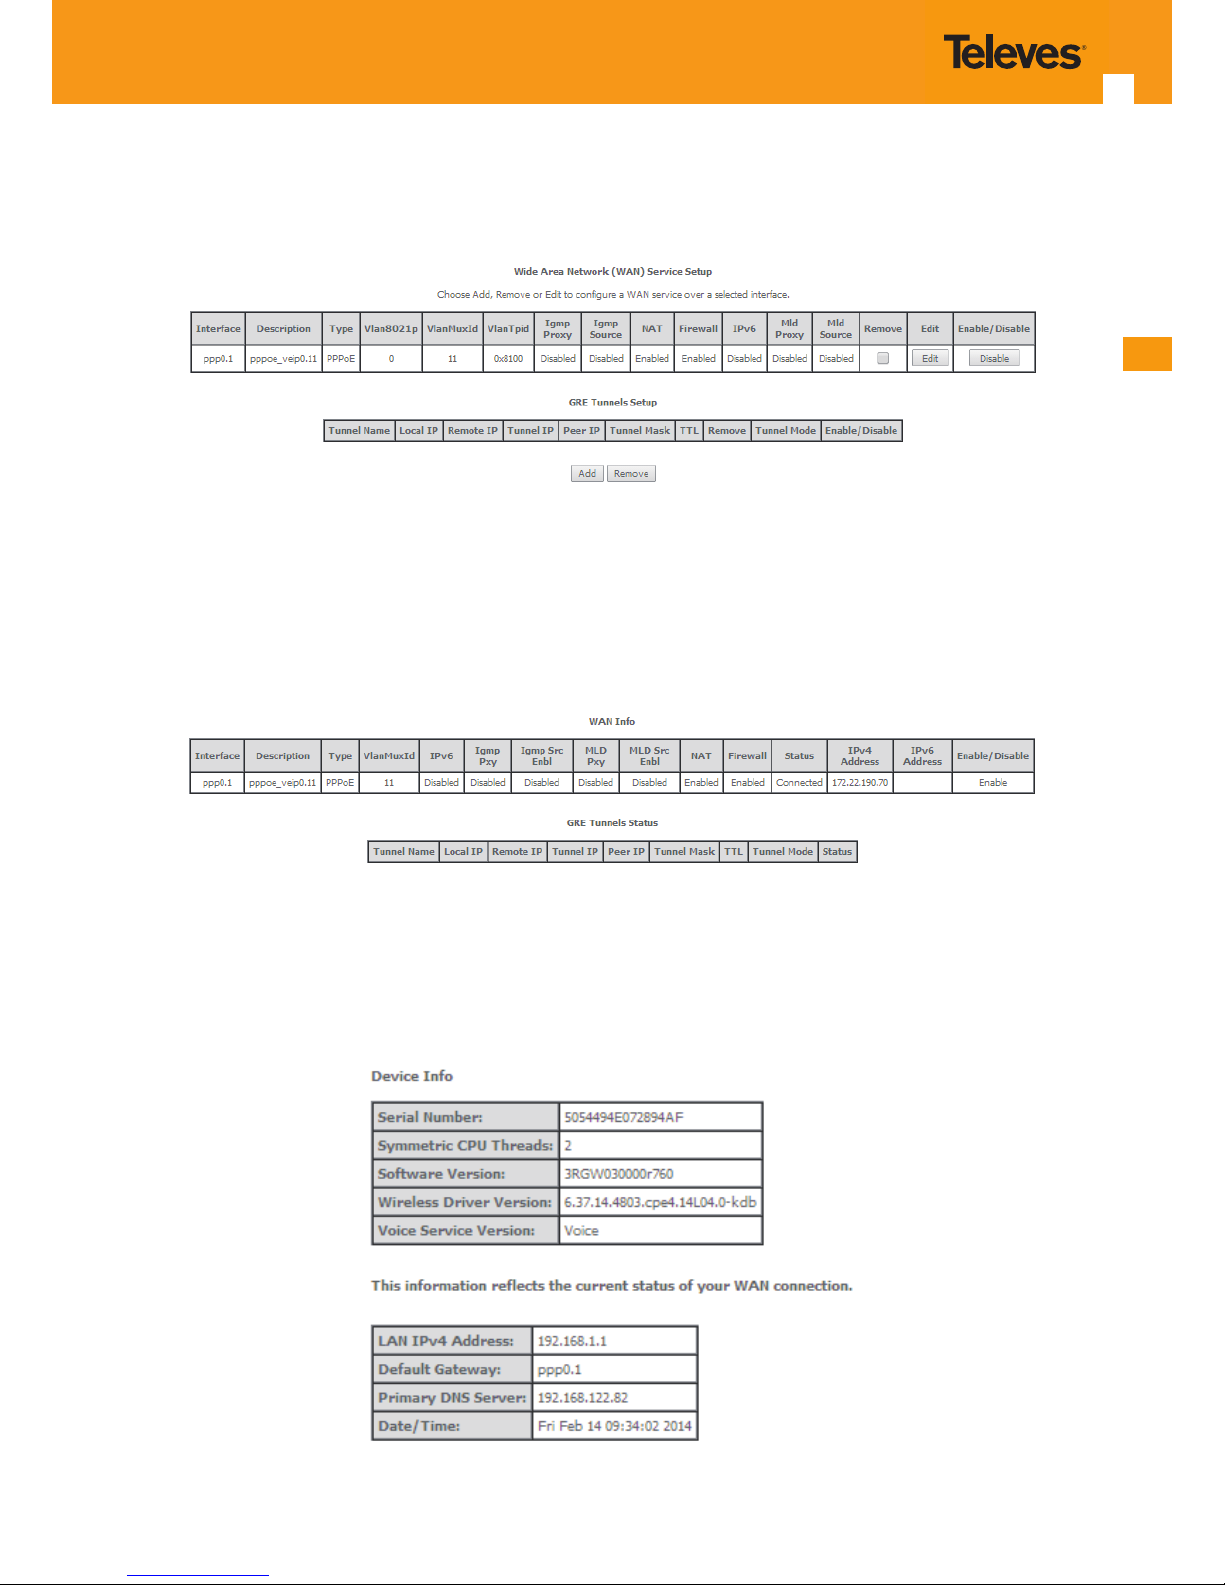
EN
59
To nalize the conguration use the Save/Apply button, Figure 5-35. The next displayed window is initial window, the WAN Service Window, where
the service congured is displayed in the corresponding table, Figure 5-36.
Figure 5-36: WAN Service Setup Initial Window- service conguration displayed
It is now possible to view the congured WAN service parameters as well as obtained IP address by Selecting the Device Info sub-menu item WAN,
Figure 5-37. Date and Hour are updated at the Device Info window, Figure 5-38.
Figure 5-37: Device Info- WAN Service Current conguration and IP Address
After WAN service conguration, the Routing table, Figure 5-39, DNS table, Figure 5-40 and Interfacer Grouping information, Figure 5-41, are updated reecting the congurations done, in this example the congured ppp0.1 interface appears in the Routing and DNS tables as the default
WAN interface and in the Interface Grouping and the default WAN interface.
Figure 5-38: Device Info- Date and hour update
Page 60
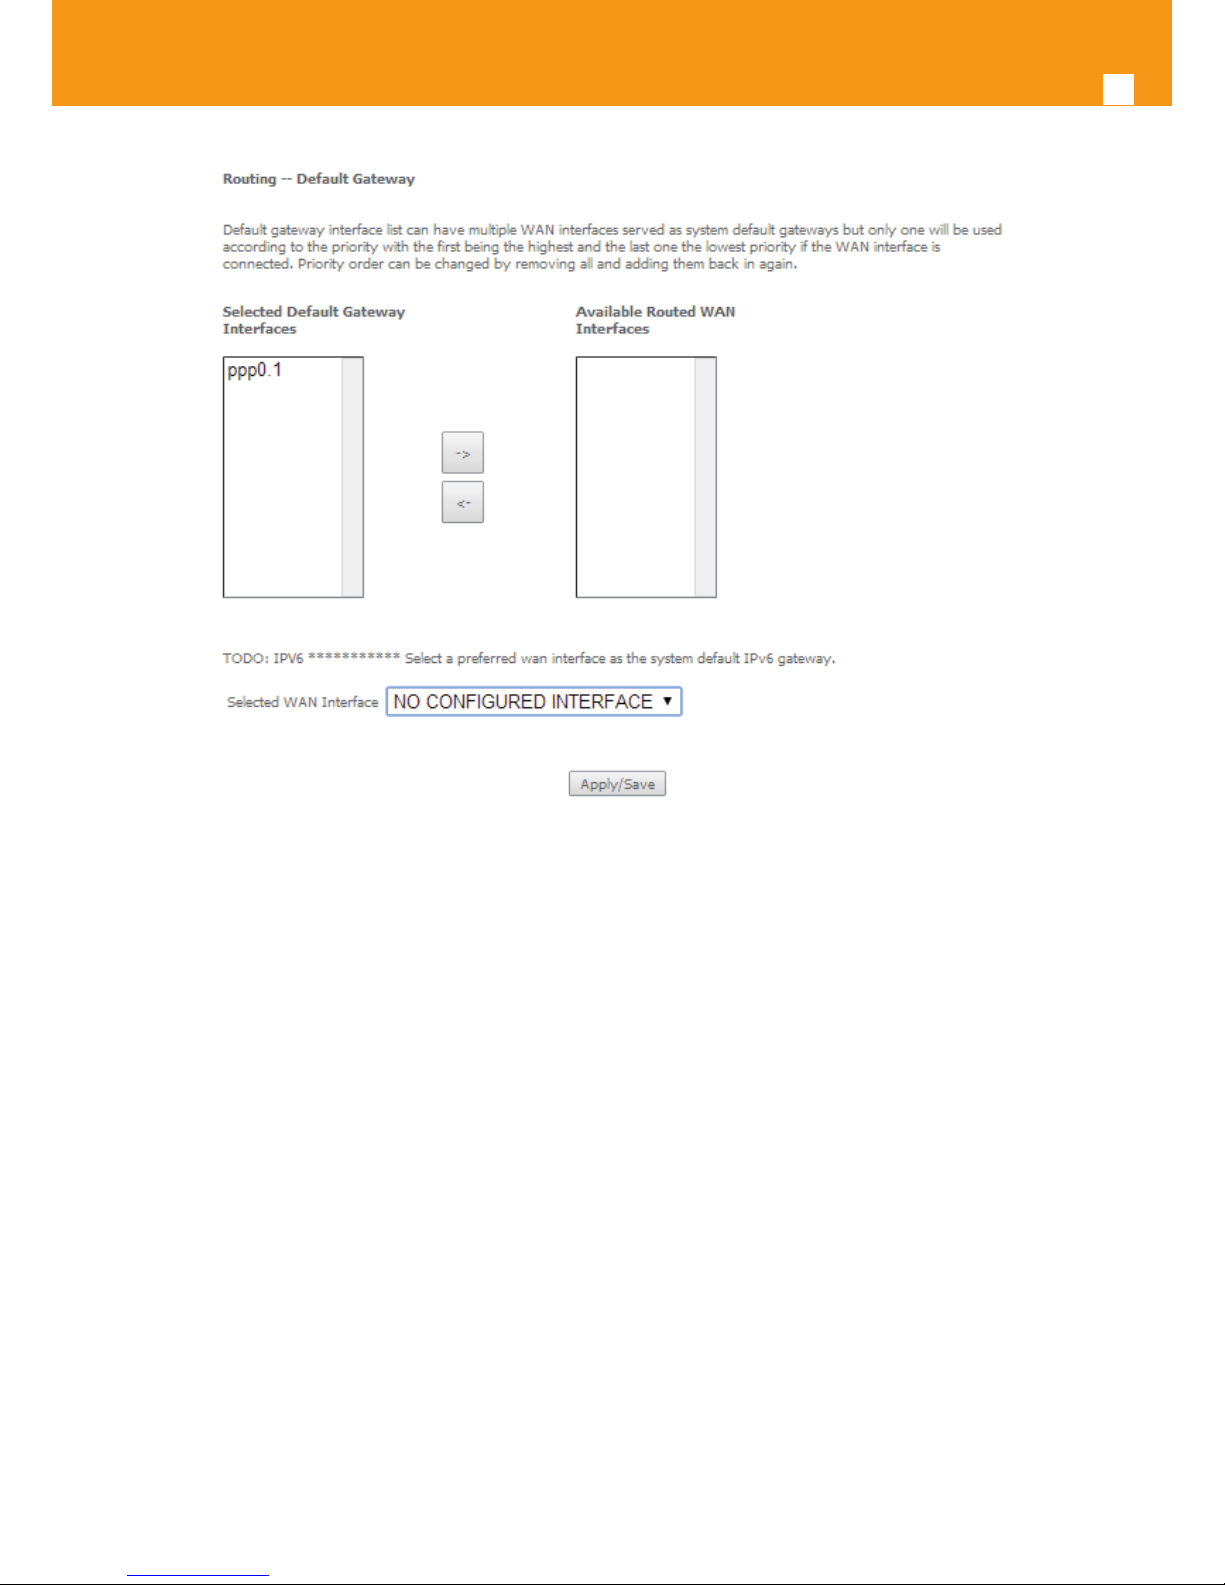
60
GPON ONT
Figure 5-39: Advanced Setup / routing - current routing table
Page 61
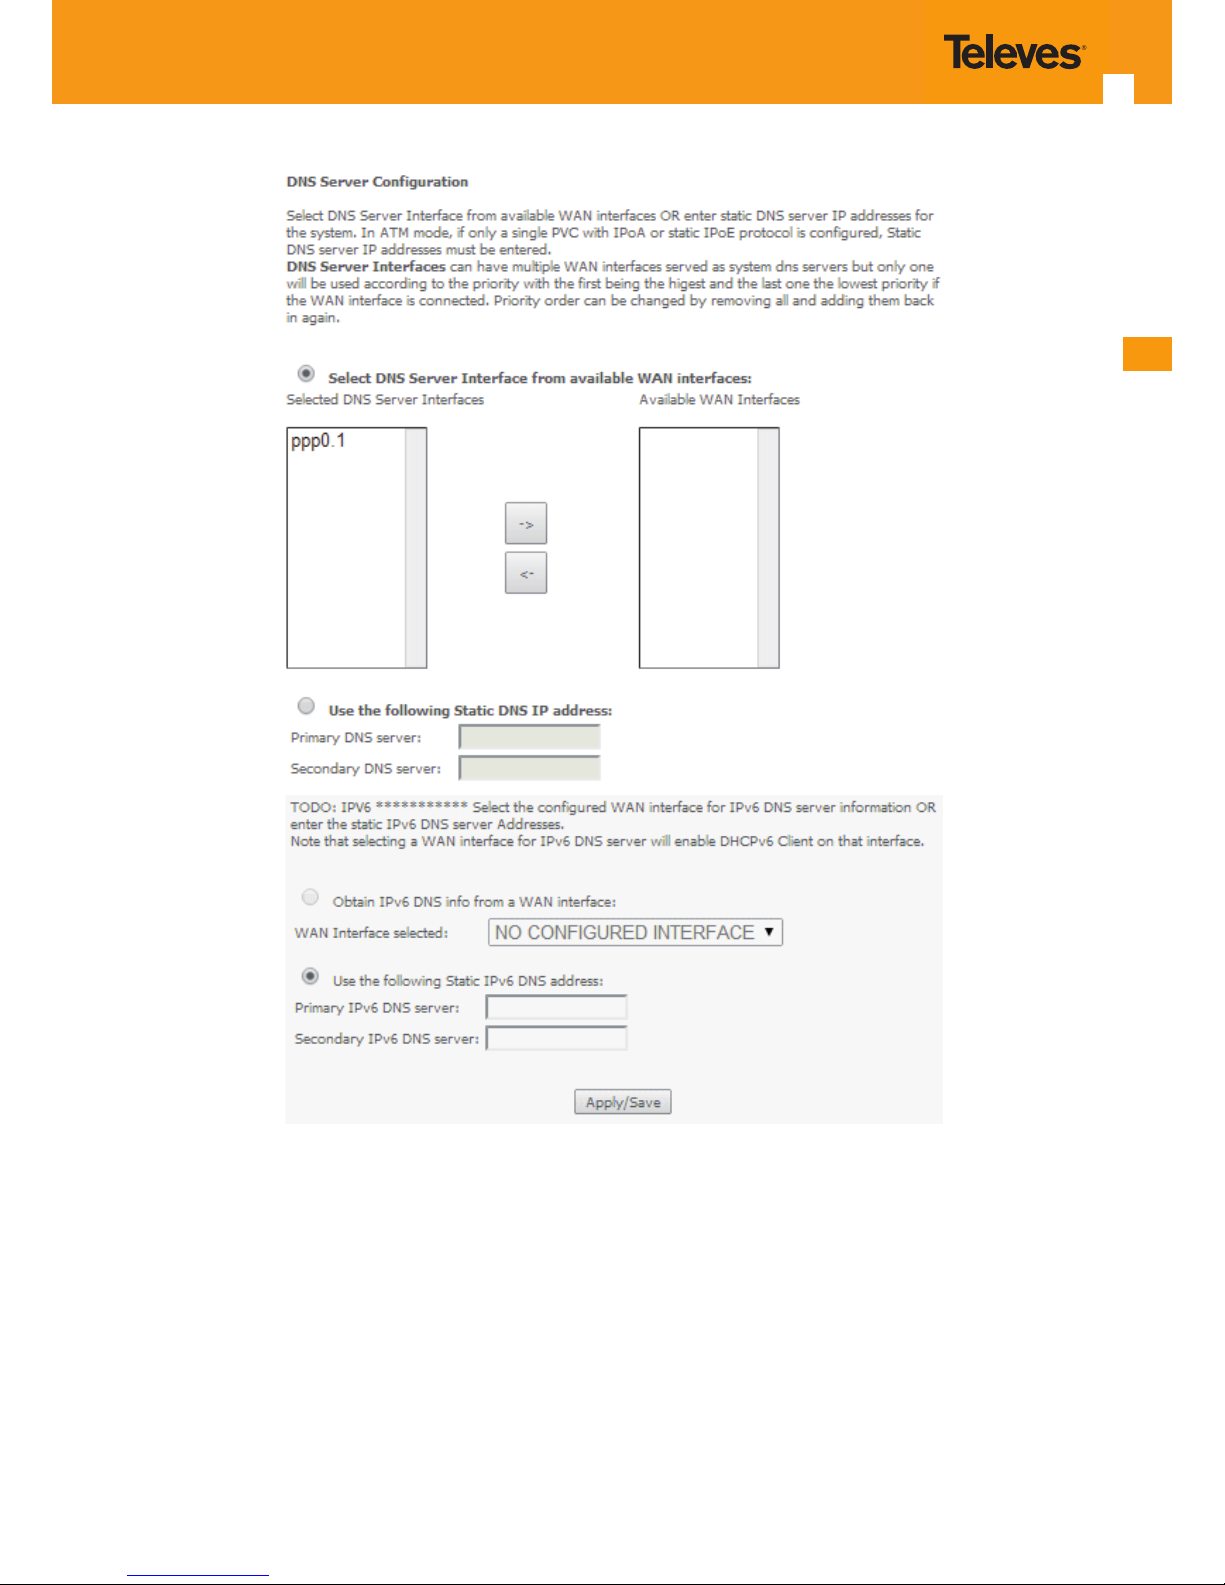
EN
61
Figure 5-40: Advanced Setup / DNS- current DNS server table
Page 62
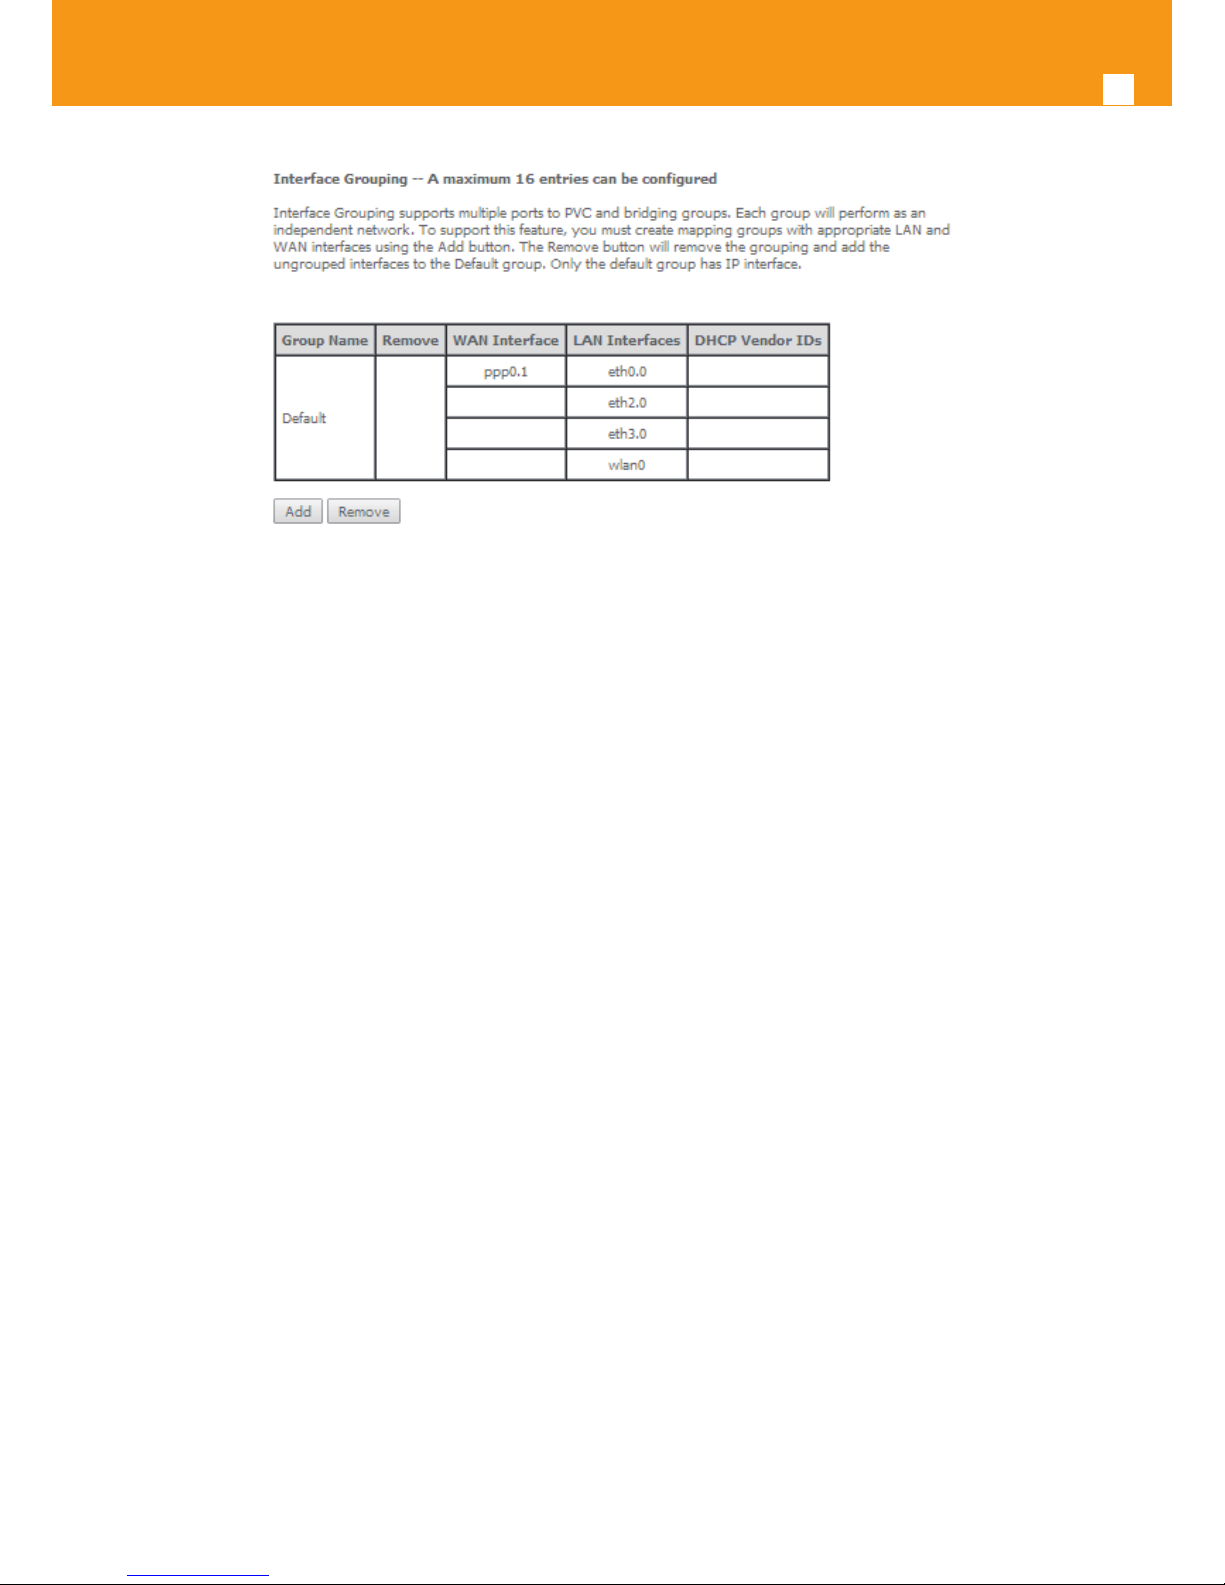
62
GPON ONT
Figure 5-41: Advanced Setup /Interface Grouping- current Interface Grouping table
5.6.2.2 IPoE Type of Service Creation
After the selection of the WAN interface associated to the service to create, Figure 5-21 and Figure 5-22 , use the Next button at Figure 5-22, to
progress to the next WAN Service setup window- Wan service Conguration, Figure 5-42.
At this window execute the following steps:
STEP 1. Select the IP over Ethernet (IPoE) WAN service type.
STEP 2. At the Field Service Description enter a string for the service description; the default service description is a string automatically
lled in when the type o device is selected(Step1) and composed by the type of Service followed by underscore and the WAN interface name , e.g. ipoe_veip0.
STEP 3 to 6. Next elds of the WAN service conguration are related to VLAN tagging conguration; please refer to section: 5.6.2.1.2 VLAN
Tagging Conguration Procedure.
STEP 7. Once the WAN service setup parameters are congure use Next button, Figure 5-42, to progress to the next WAN Service setup
window- WAN IP Settings conguration, Figure 5-43.
Page 63
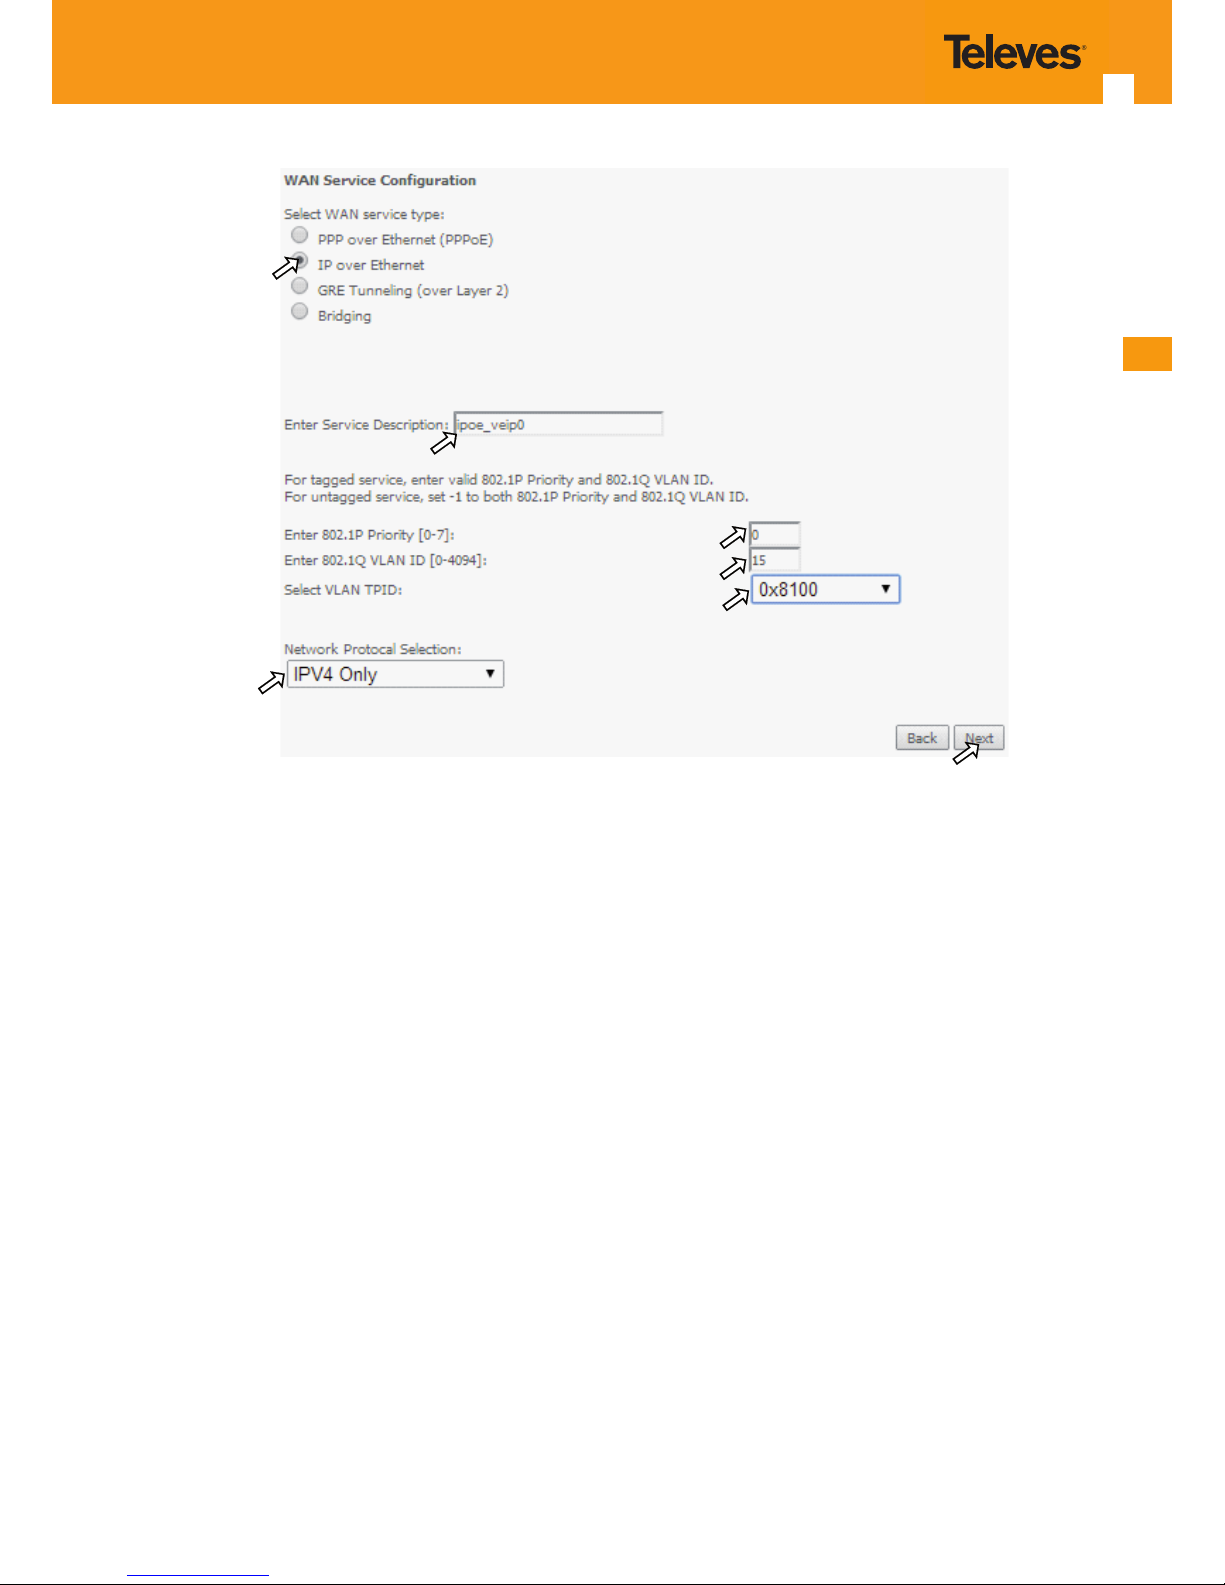
EN
63
1
2
3
4
5
6
7
Figure 5-42: WAN service setup-type of service selection and service conguration – IPoE service
5.6.2.2.1 WAN IP Settings
WAN IP Settings should use the information provided by the ISP.
IP address can be obtained automatically via DHCP or can be statically congured.
5.6.2.2.1.1 Obtain IP Address Automatically
STEP 1. Select the option “Obtain an IP address automatically, option 1 of Figure 5-43.
STEP 2. DHCP will be used to obtain an IP address; there are 4 DHCP options that can be congured:
Option 60 Vendor ID: String value; this option allows the identication of the vendor by the DHCP server and is used in this
context to identify in the DHCP server the IP Address pool to use by the congured service.
Option 61- IAID (Identity Association Identier):value-8 hexadecimal digits; IAID is a binding between an interface and
one or more IP addresses – this option used with DUID allows to identify an interface in a client to which will be attributed a
temporary IP address by DHCPv6
Option 61- DUID (DHCP Unique Identier): value -1 hexadecimal digit; this option identies a DHCPv6 participant; each allocation in the DHCPv6 server is identied by a DUID and an IAID
Option 125 Vendor Identifying – Vendor Options: Fag –Enable/disable; the denition of the information carried in this option is vendor specic. Use of vendor-specic information allows enhanced operation, utilizing additional features in a vendor’s
DHCP implementation.
Page 64
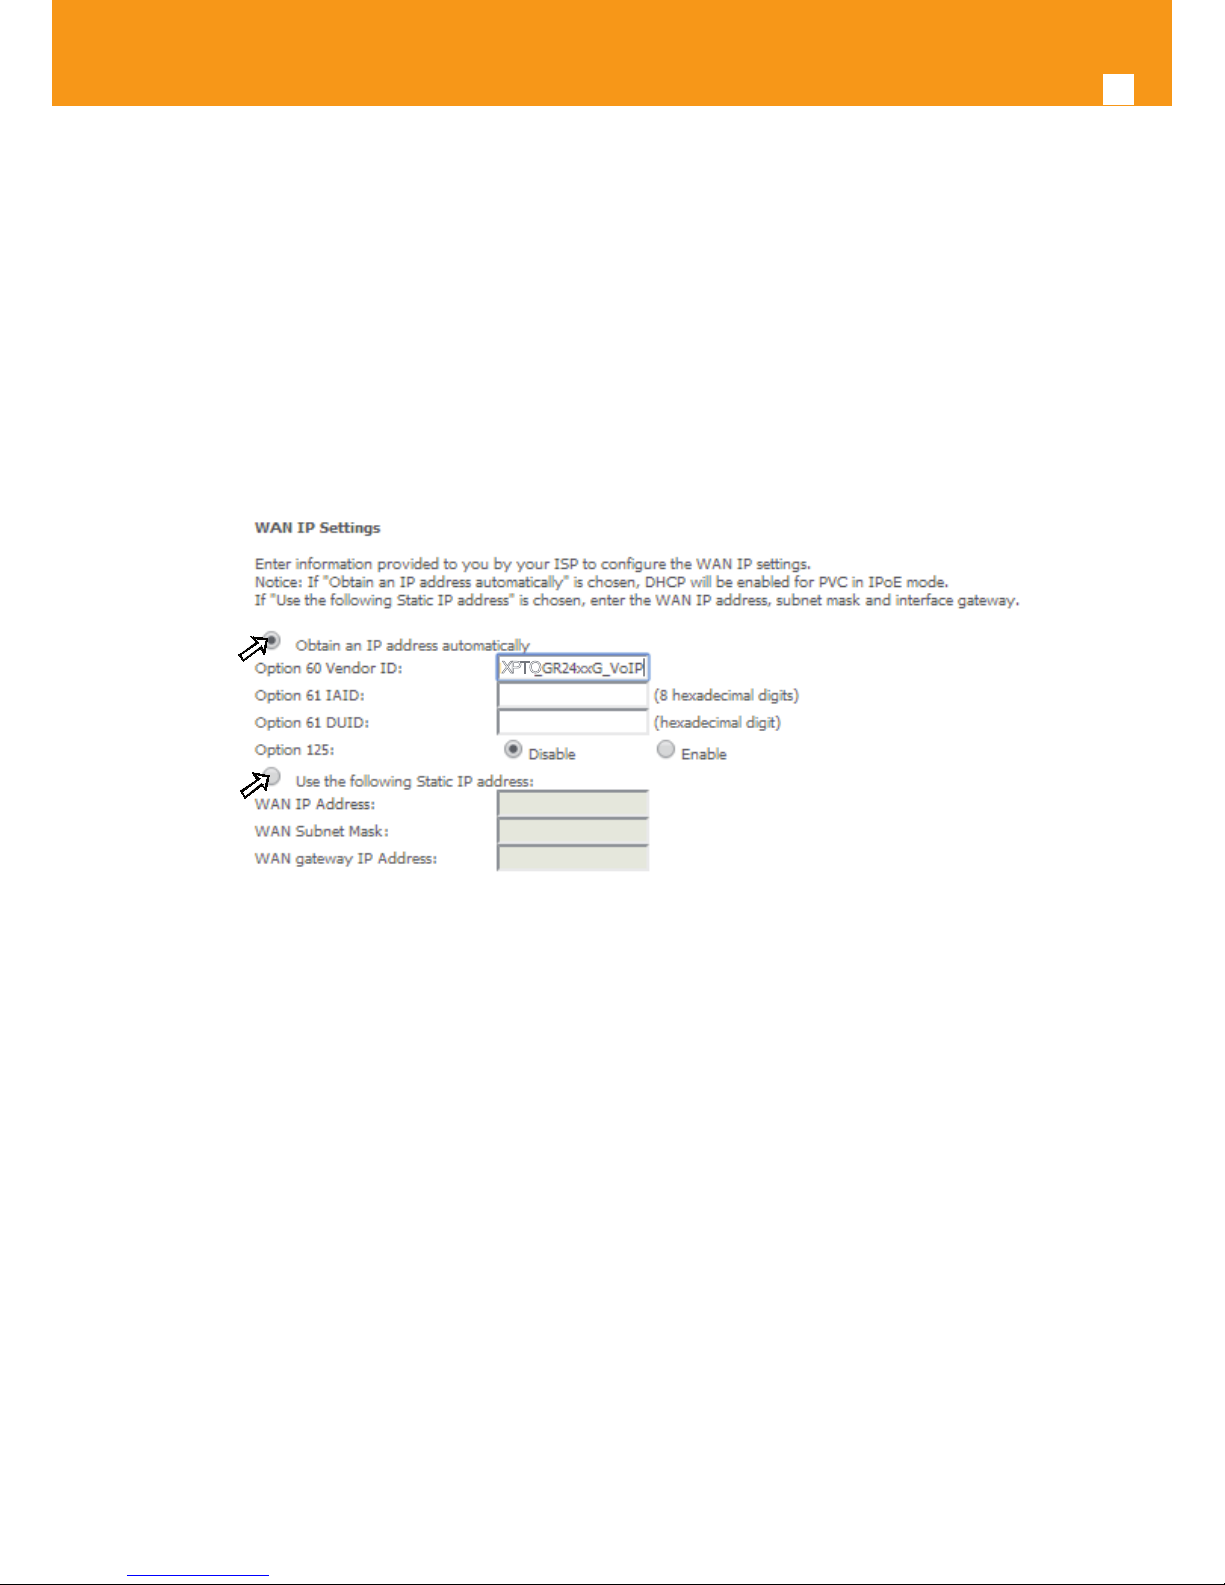
64
GPON ONT
5.6.2.2.1.2 Use of Static IP Address
STEP 1. Select the option “Use the following Static IP address “, option 2 of Figure 5-43.
STEP 2. Enter WAN IP address to be used
Enter WAN Subnet Mask to be used;
Enter WAN gateway IP Address to be used
STEP 3. Use the Next button to progress to the WAN Service setup window- Network Address Translation Settings conguration
1
2
XPTO
Figure 5-43: WAN Service setup window- WAN IP Settings conguration
5.6.2.2.2 Network Address Translation Settings
To use NAT, option “Enable NAT” must be selected, Figure 5-44; If NAT option is selected, the option Fullcone NAT is available; if selected a warning
message on the disadvantages of its use is shown, Figure 5-45.
To use Firewall option “Enable Firewall” must be selected, Figure 5-44.
In this window is also possible to congure IGMP Multicast as Proxy by selecting option “Enable IGMP Multicast Proxy” or as a Source by selecting
option “Enable IGMP Multicast Source” and enable/disable Multicast VLAN lter, Figure 5-46.
ArPing Setup allows ArPing to be enabled and the number of repetitions and timeout to be congured. To congure ArPing “Enable ArPing” Option must be selected, Figure 5-47, and the values for number o repetitions and timeout interval (seconds) must be entered. ArPing is similar to
Ping as given an IP address it test to nd out if this is in use on the local network, and can get additional information about the device using that
address.
Page 65
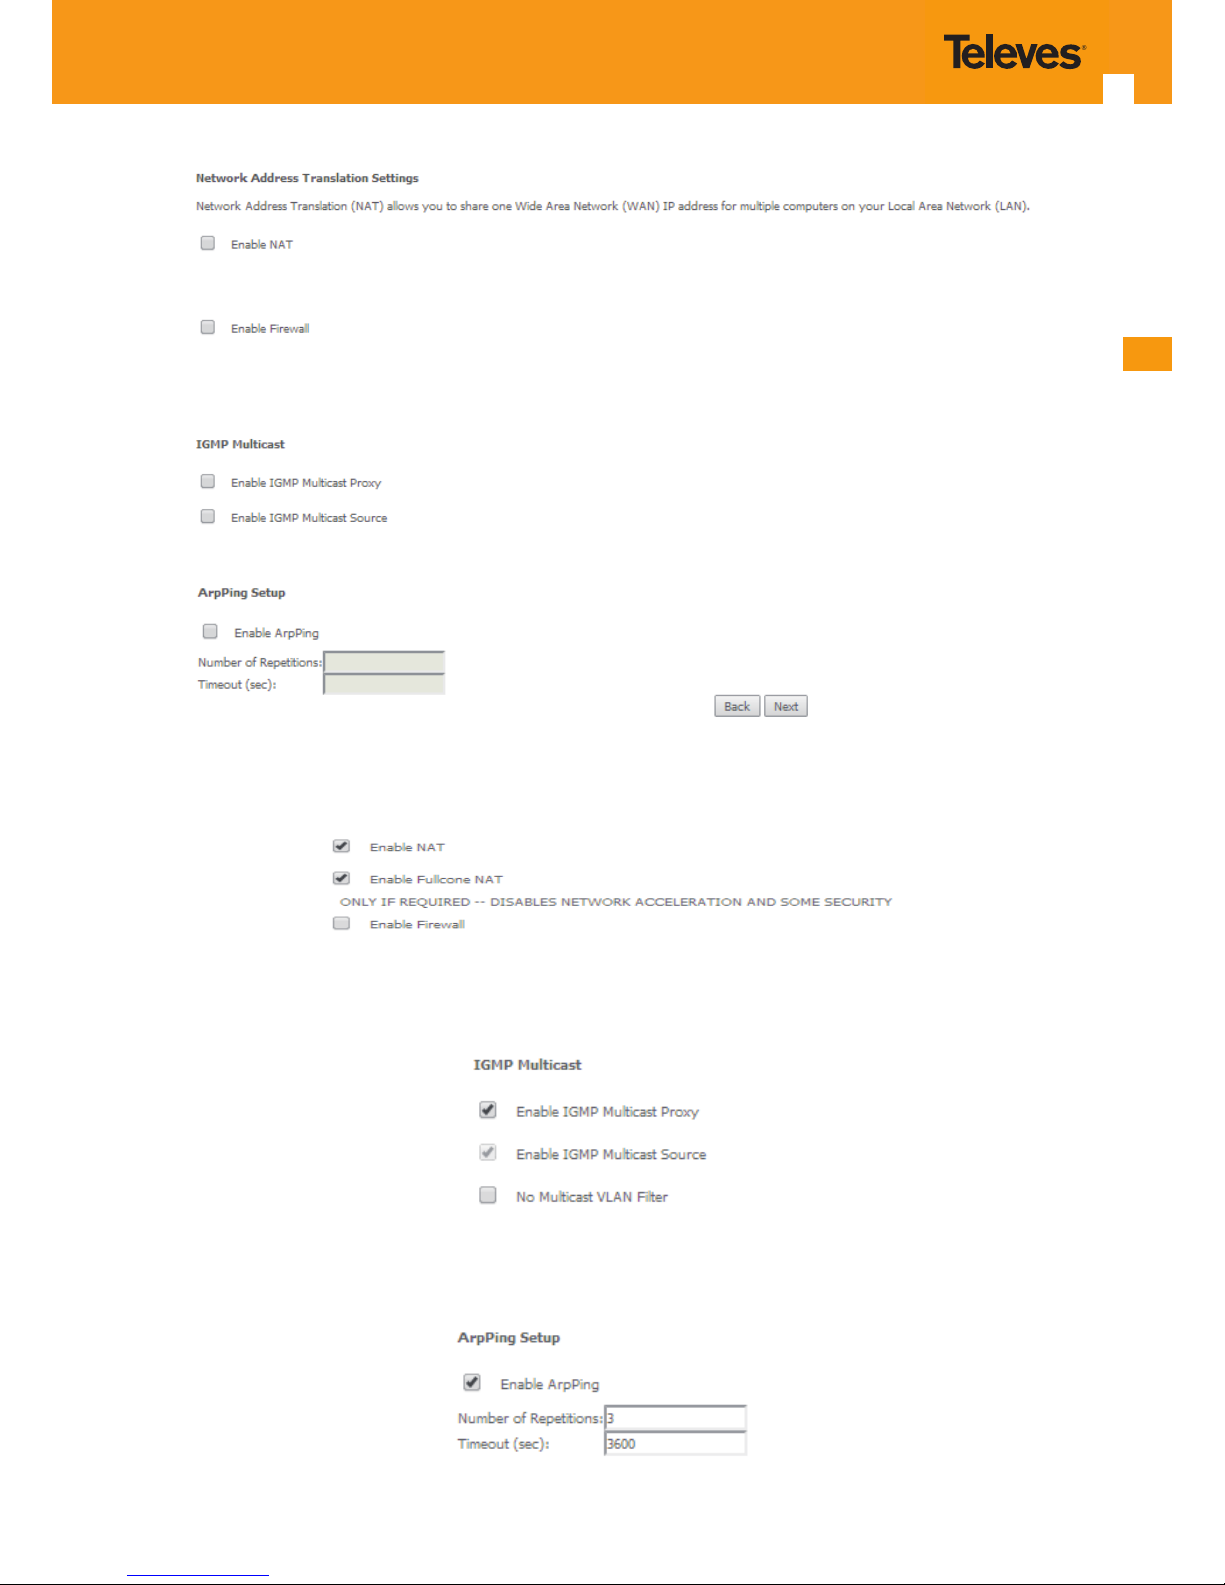
EN
65
Figure 5-44: WAN Service setup window- NAT, IGMP and Arping Settings conguration
Figure 5-45: WAN Service setup window- Network Address Translation Settings conguration Enable fullcone NAT warning message
Figure 5-46: WAN Service setup window- IGMP Multicast conguration options
Figure 5-47: WAN Service setup window- ArPing Setup
Page 66
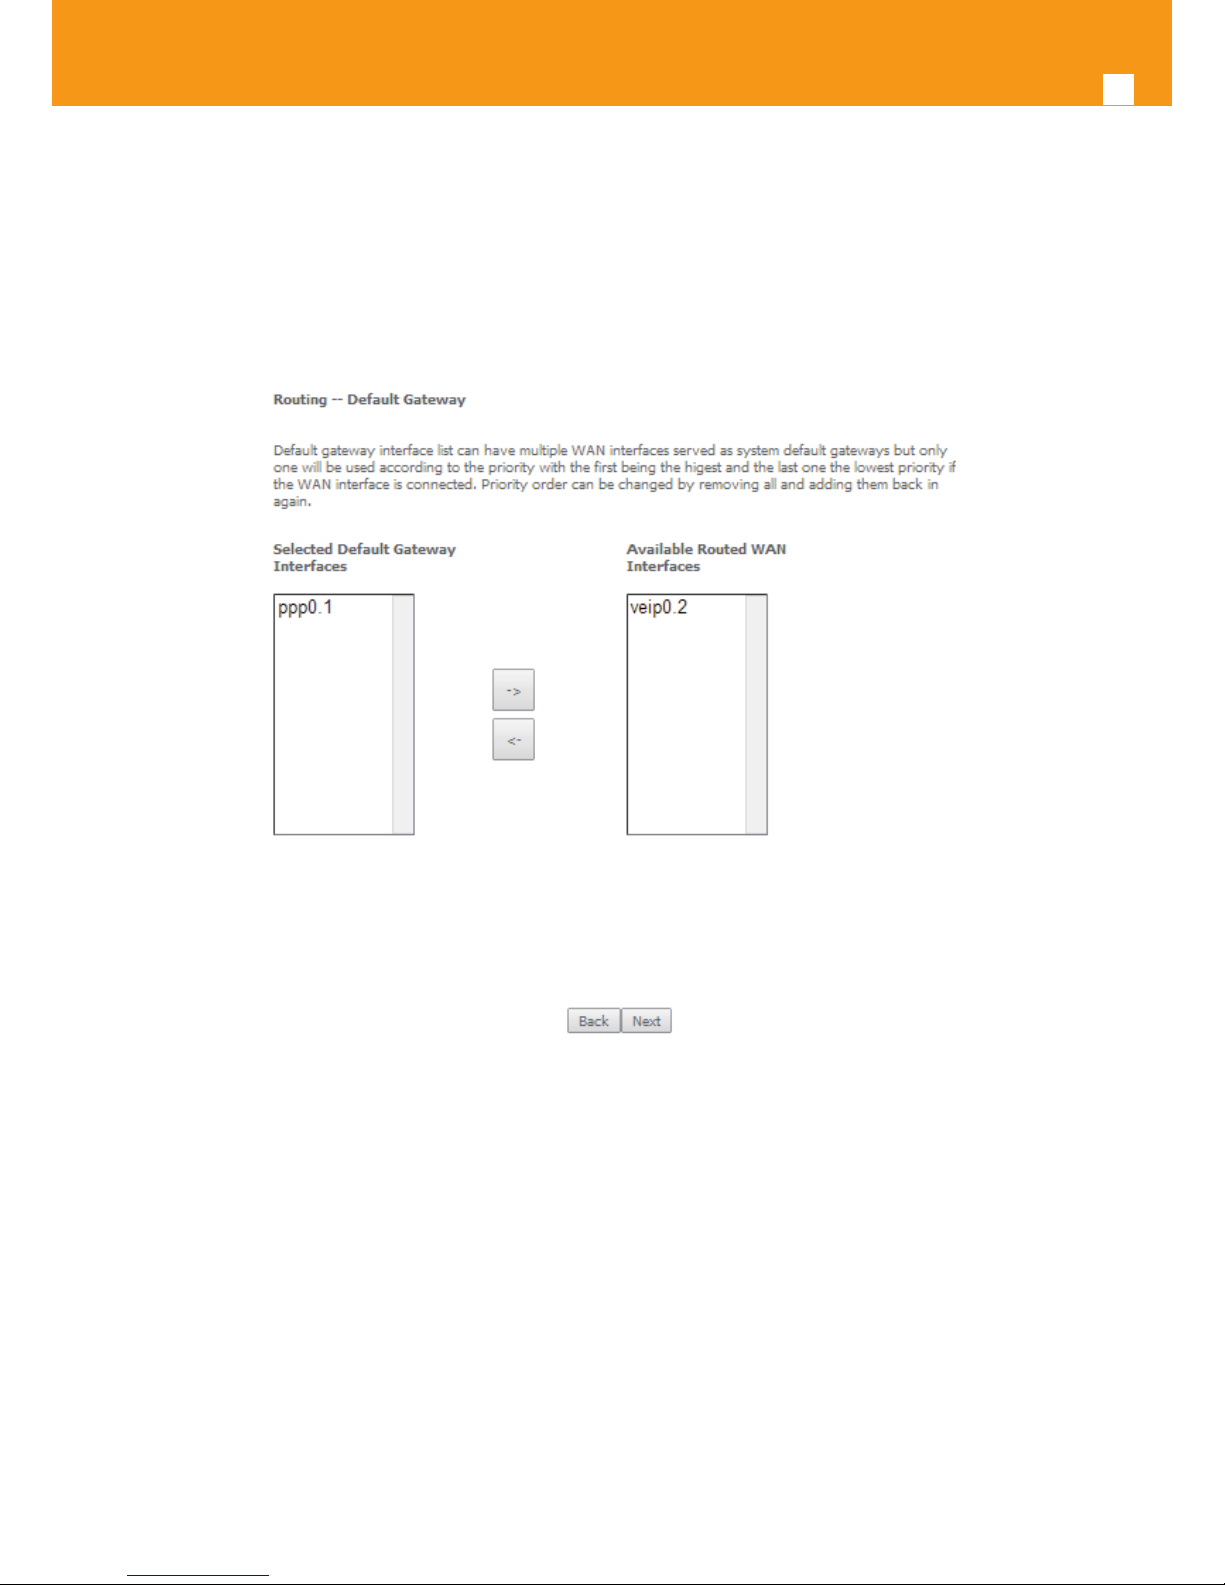
66
GPON ONT
Once the NAT, IGMP and Arping Settings are congured use Next button Figure 5-44, to progress to the next WAN Service setup - Routing Default
Gateway conguration window, Figure 5-48.
The actual default gateway conguration is presented in this window, with the ppp0.1 WAN interface previously congured shown as the default
Gateway interface. In the list of available WAN routed interfaces the veip0.2 used in this IPoE service conguration is shown, Figure 5-48, and can
be used to change/update default Routing Default Gateway current conguration.
Please refer to section 5.6.2.1.4 Routing Default Gateway Conguration, for the explanation of the conguration.
Figure 5-48: WAN Service setup - Routing Default Gateway conguration window
After default gateway interface conguration, use the Next button, Figure 5-48, to progress to the next WAN Service setup – DNS Server conguration parameters window, Figure 5-49.
DNS table, as well as previously shown Routing table, is in accordance with current Default Gateway conguration, Figure 67: ppp0.1 is thus shown
as the current DNS server interface, but veip0.2 WAN interface is available for changing/updating DNS server interface if desired.
Please refer to section 5.6.2.1.5 DNS Server Conguration, for the explanation of the conguration.
Page 67
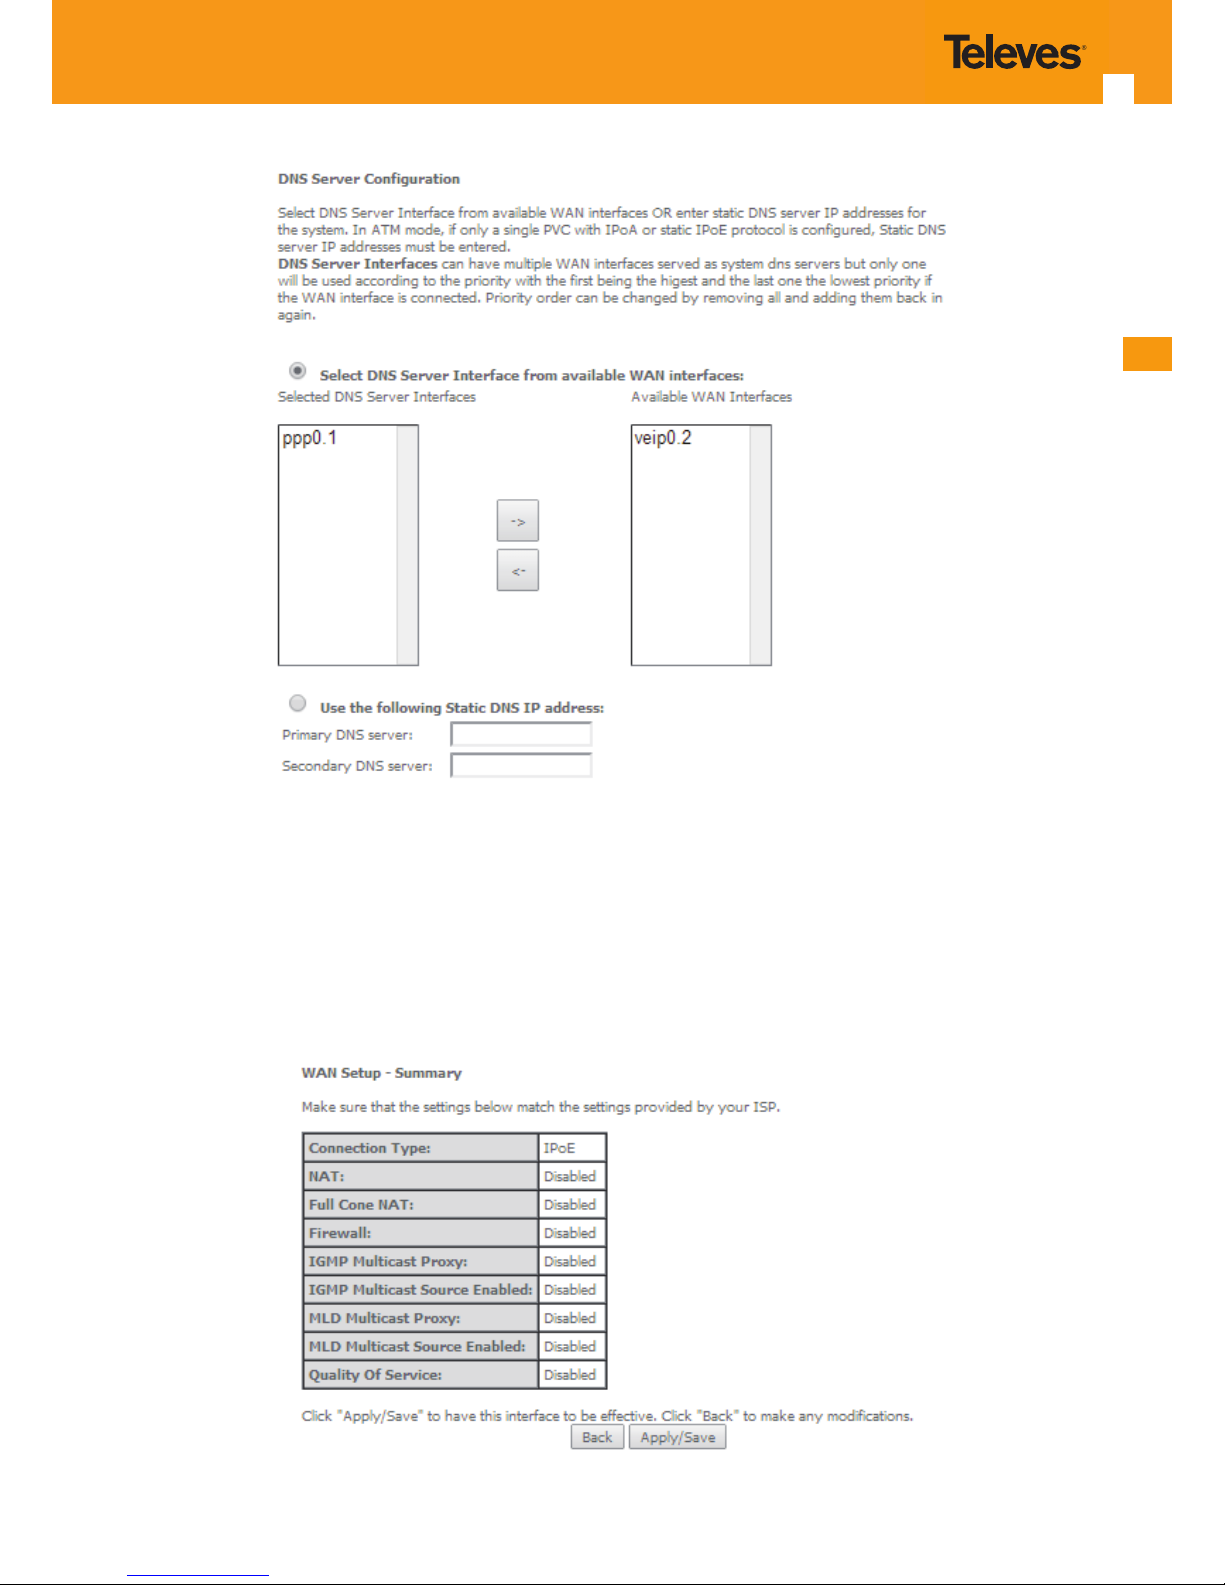
EN
67
Figure 5-49: WAN Service setup – DNS Server conguration parameters window
Once the DNS server conguration is done the IPoE WAN service conguration is complete. Use the Next button to progress to the WAN Service
Setup Summary window, Figure 5-50. This table should reect the conguration for the WAN service setup parameters than have been entered on
the successive WAN service setup conguration windows. Network Address Translation ag and Firewall ag default congurations are enabled.
Please verify the presented conguration match the settings provided by the ISP for this service.
Figure 5-50: WAN Service Setup Summary window- IPoE service congured
Page 68
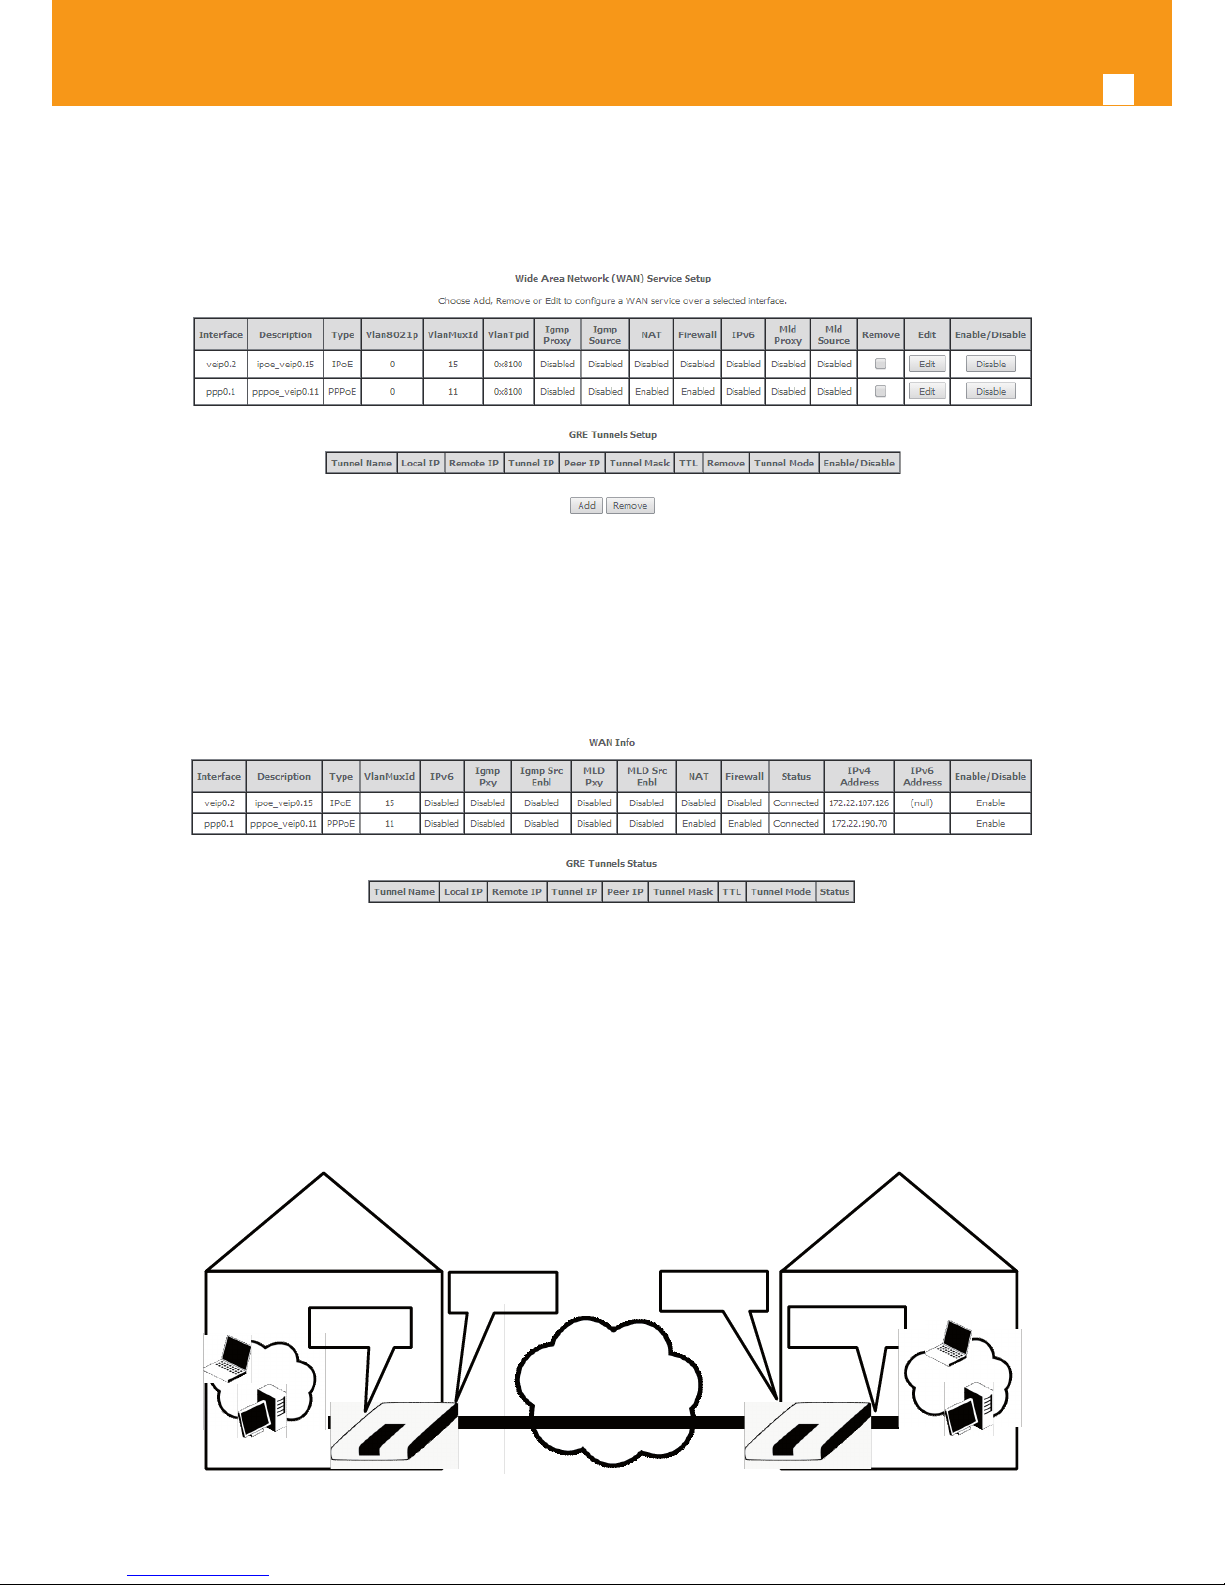
68
GPON ONT
To nalize the conguration use the Save/Apply button, Figure 5-50. The next displayed window is initial window, the WAN Service Window, where
the service congured is displayed in the corresponding table, Figure 5-51.
Figure 5-51: WAN Service Setup Initial Window- service conguration displayed
It is now possible to view the currently congured WAN services’ parameters as well as obtained IP addresses by Selecting the Device Info submenu item WAN, Figure 5-52.
Figure 5-52: Device Info-WAN Service Current conguration and IP Addresses
5.6.2.3 GRE Type of Service Creation
A GRE tunnel conguration example will be given, showing the GRE tunnel settings conguration at the Network A Refs. 769501-769502.
Internet
ONT-RGW
ONT-RGW
Network A
Network B
GRE Tunnel
Public IP
172.22.107.5
Public IP
172.22.107.4
Tunnel Interface
10.10.10.1
Tunnel Interface
10.10.10.2
Figure 5-53: GRE Tunnel conguration example ate the Network A Refs. 769501-769502
Page 69
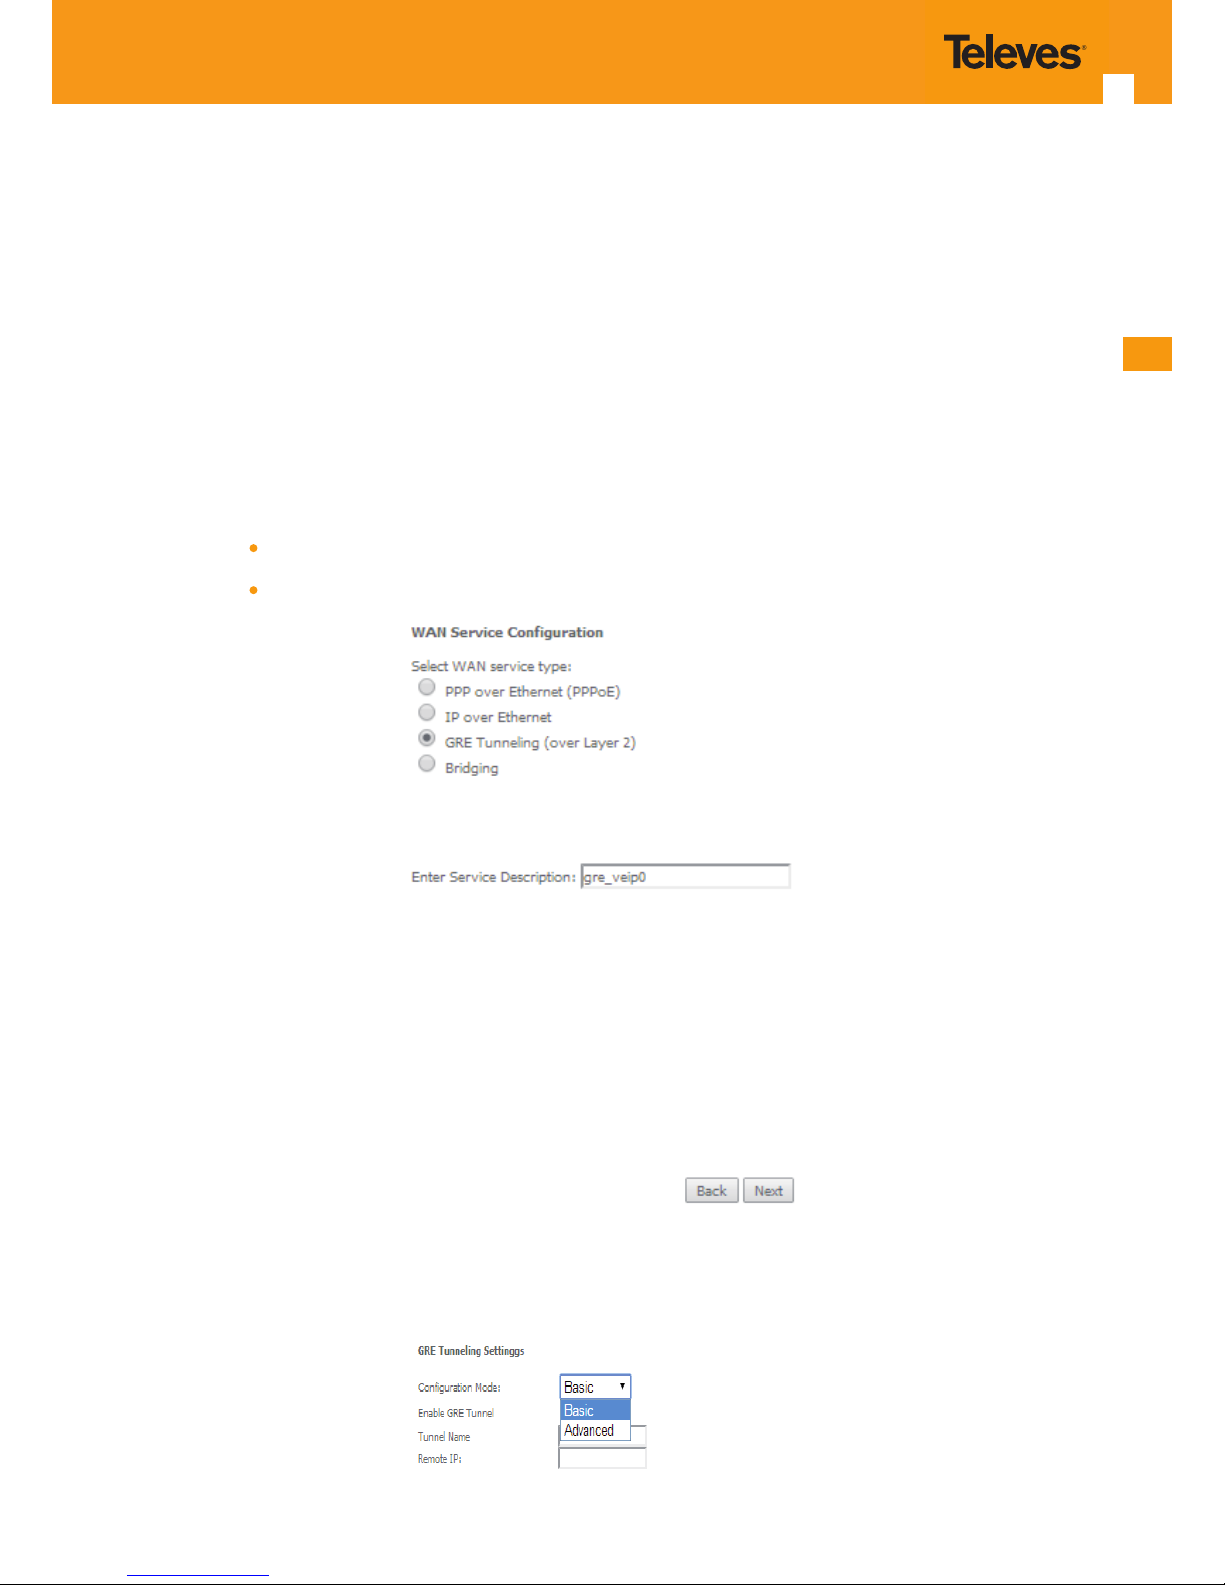
EN
69
After the selection of the WAN interface associated to the service to create, Figure 5-21 and Figure 5-22, use the Next button at Figure 5-22, to
progress to the next WAN Service setup window- Wan service Conguration, Figure 5-54.
At this window execute the following steps:
STEP 1. Select the IP over Ethernet (GRE) WAN service type, Figure 5-54.
STEP 2. It the Field Service Description enter a string for the service description; the default service description is a string automatically lled
in when the type o device is selected (Step1) and composed by the type of Service followed by underscore and the WAN interface
name , e.g. gre_veip0.
STEP 3. Use the Next button, Figure 5-54, to progress to the WAN Service setup window- GRE Tunneling Settings, Figure 5-55.
In this window two GRE conguration modes are available from a conguration mode combo box selection, ; The detail of the re-
quired information for setting the GRE will vary according to the conguration mode selected:
Basic
Advanced
Figure 5-54: WAN service setup – type of service selection and service conguration – GRE service
Figure 5-55: WAN Service setup window- GRE Tunneling Settings
Page 70
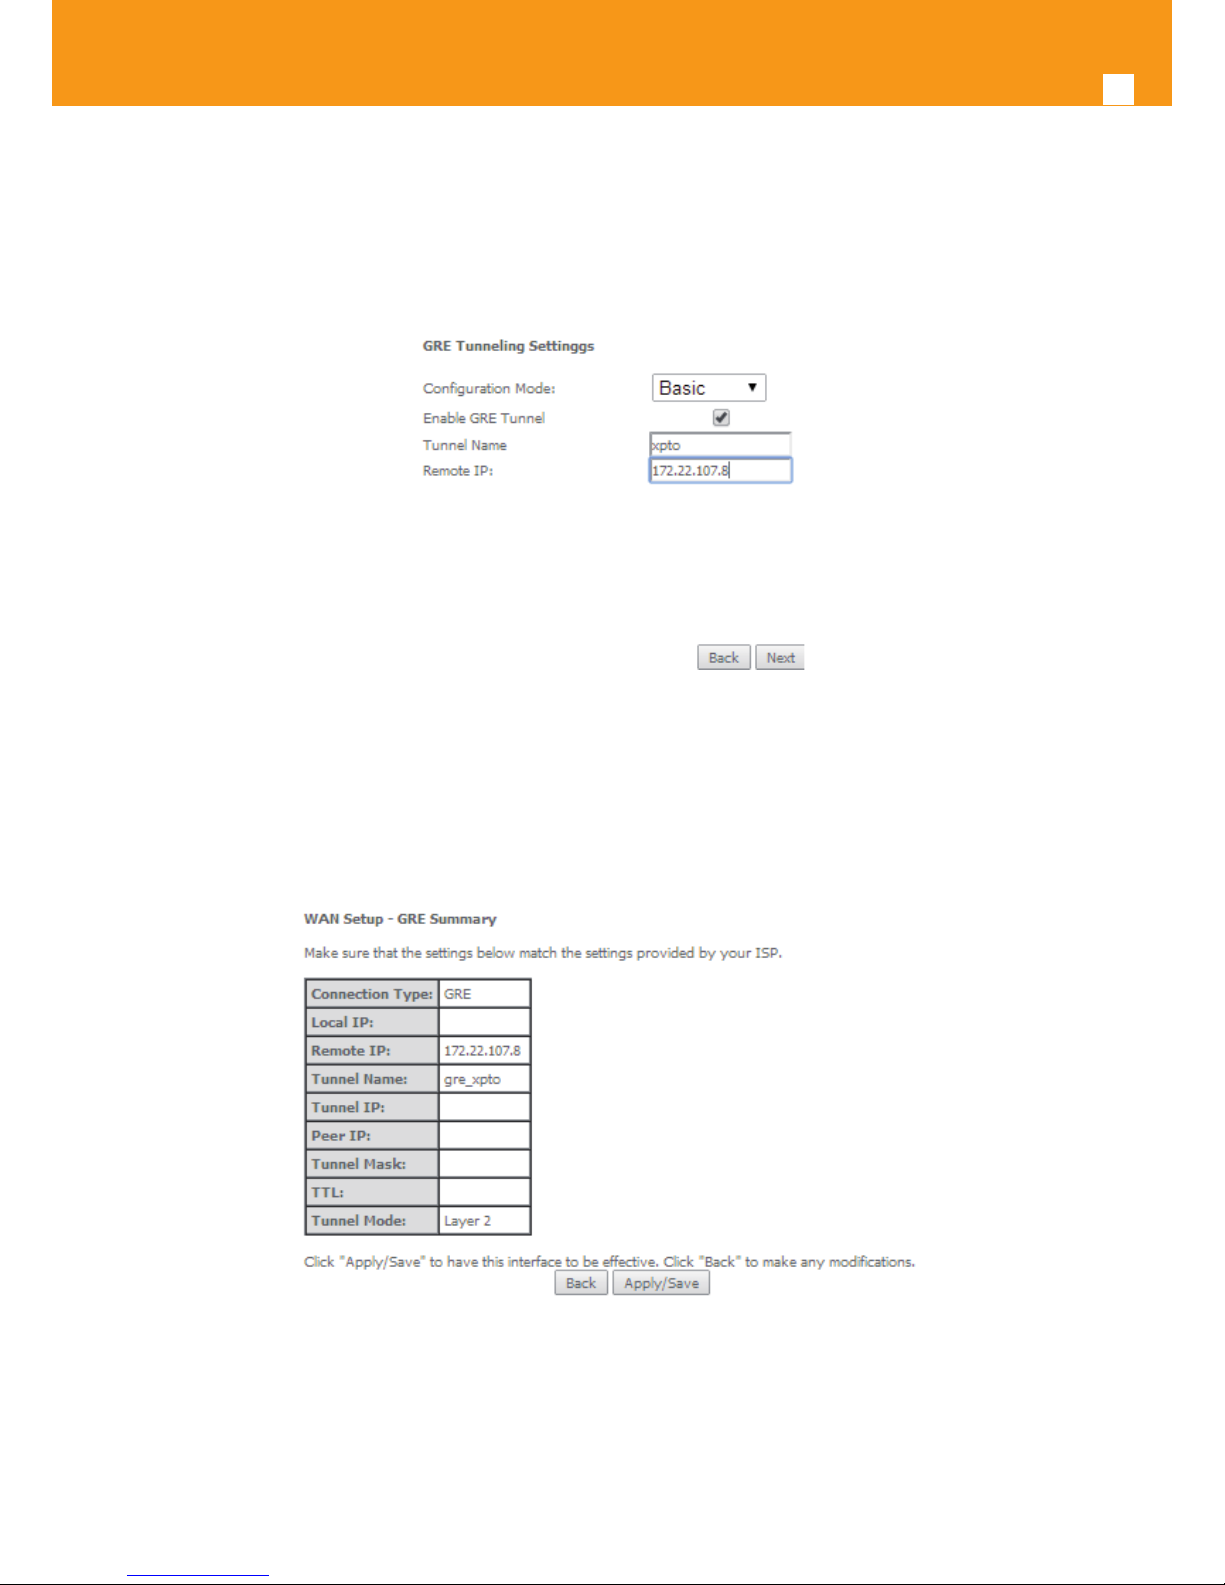
70
GPON ONT
5.6.2.3.1 GRE Tunnel Setting – Basic Conguration Mode
In the basic conguration mode only Tunnel Name and Remote IP are required for setting the GRE Tunnel, Figure 5-56. Remote IP is the Public
IP address of the routing device terminating the GRE Tunnel in the other extreme of the tunnel (Refs. 769501-769502 of network B in the shown
example), Figure 5-53.
Figure 5-56: WAN Service setup window - GRE Tunneling Settings – Basic conguration mode
After entering the required information, use Next button to progress to the next window, WAN Service setup window- GRE Tunneling Settings –
GRE Summary, Figure 5-57. This table should reect the conguration for the GRE-Tunnel service setup parameters than have been congured.
Please verify the presented conguration match the settings provided by the ISP for this service.
Figure 5-57: WAN Service setup window- GRE Tunneling Settings – GRE Summary
To nalize the conguration use the Save/Apply button, Figure 5-57. The next displayed window is initial window, the WAN Service Window, where
the service congured is displayed in the corresponding table, Figure 5-58.
Page 71
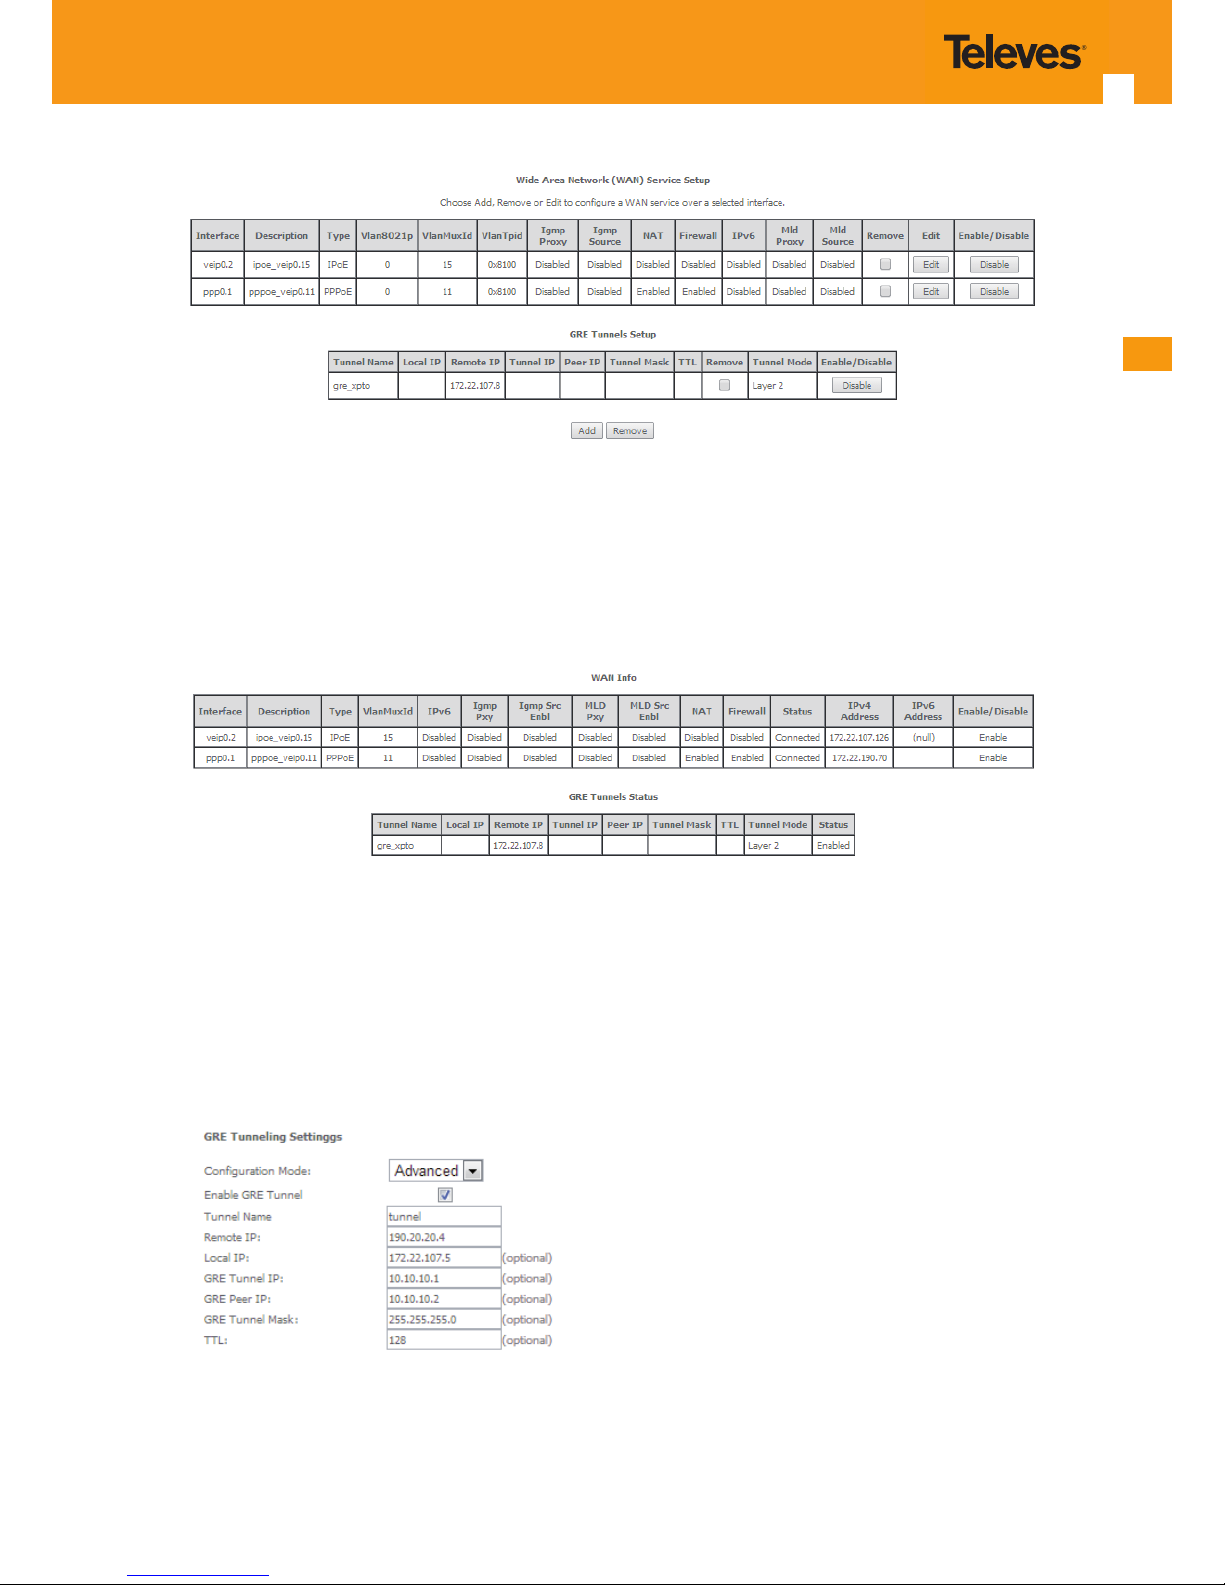
EN
71
Figure 5-58: WAN Service Setup Initial Window- service conguration displayed
It is now possible to view the currently congured WAN services’ parameters as well as obtained IP addresses by Selecting the Device Info submenu item WAN, Figure 5-59.
Figure 5-59: Device Info- WAN service Current conguration
5.6.2.3.2 GRE Tunnel Setting – Advanced Conguration Mode
In the Advanced conguration mode the following information is required for setting the GRE Tunnel, Figure 5-56, Figure 5-60, and Table 5-14.
Figure 5-60: WAN Service setup window- GRE Tunn
Page 72
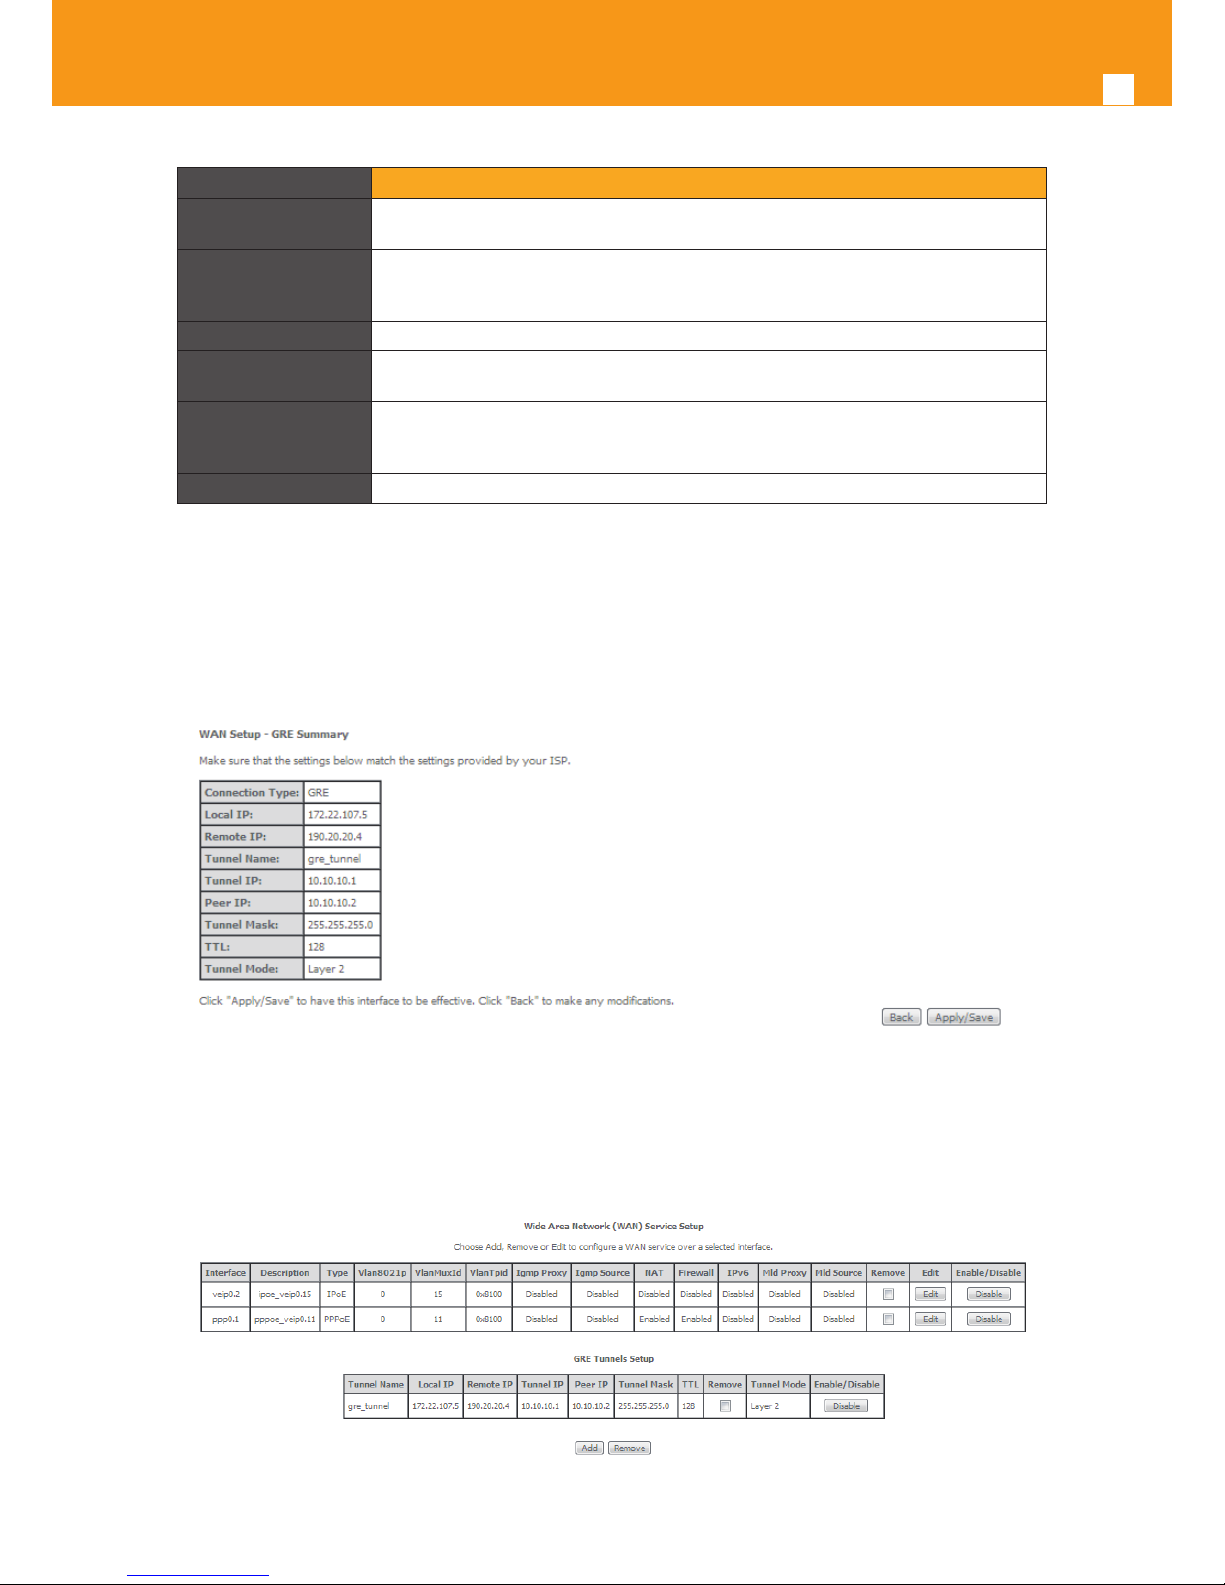
72
GPON ONT
Parameter Description
Local IP
Public IP address of the routing device where the tunnel is being congured, (Refs.
769501-769502 of network A in the shown example), Figure 5-53.
Remote IP
Public IP address of the routing device terminating the GRE Tunnel in the other extreme of the tunnel (Refs. 769501-769502 of network B in the shown example), Figure 5-53.
Tunnel Name GRE Tunnel Identication (string)
GRE Tunnel IP
IP address of GRE Tunnel interface, on the routing device being congured (Refs.
769501-769502 of network A in the shown example), Figure 5-53.
GRE Tunnel Mask
IP address of GRE Tunnel interface, on the routing device terminating the GRE Tunnel
in the other extreme of the tunnel (
Refs. 769501-769502 of network B in the shown
example), Figure 5-53.
TTL Time to Live value
Table 5-14:GRE Tunneling Settings – Advanced conguration mode parameters
After entering the required information, use Next button to progress to the next window, WAN Service setup window- GRE Tunneling Settings –
GRE Summary, Figure 5-61. This table should reect the conguration for the GRE-Tunnel service setup parameters than have been congured.
Please verify the presented conguration match the settings provided by the ISP for this service.
Figure 5-61: WAN Service setup window- GRE Tunneling Settings – GRE Summary
To nalize the conguration use the Save/Apply button, Figure 5-61. The next displayed window is initial window, the WAN Service Window, where
the service congured is displayed in the corresponding table, Figure 5-62.
Figure 5-62: WAN Service Setup Initial Window- service conguration displayed
Page 73
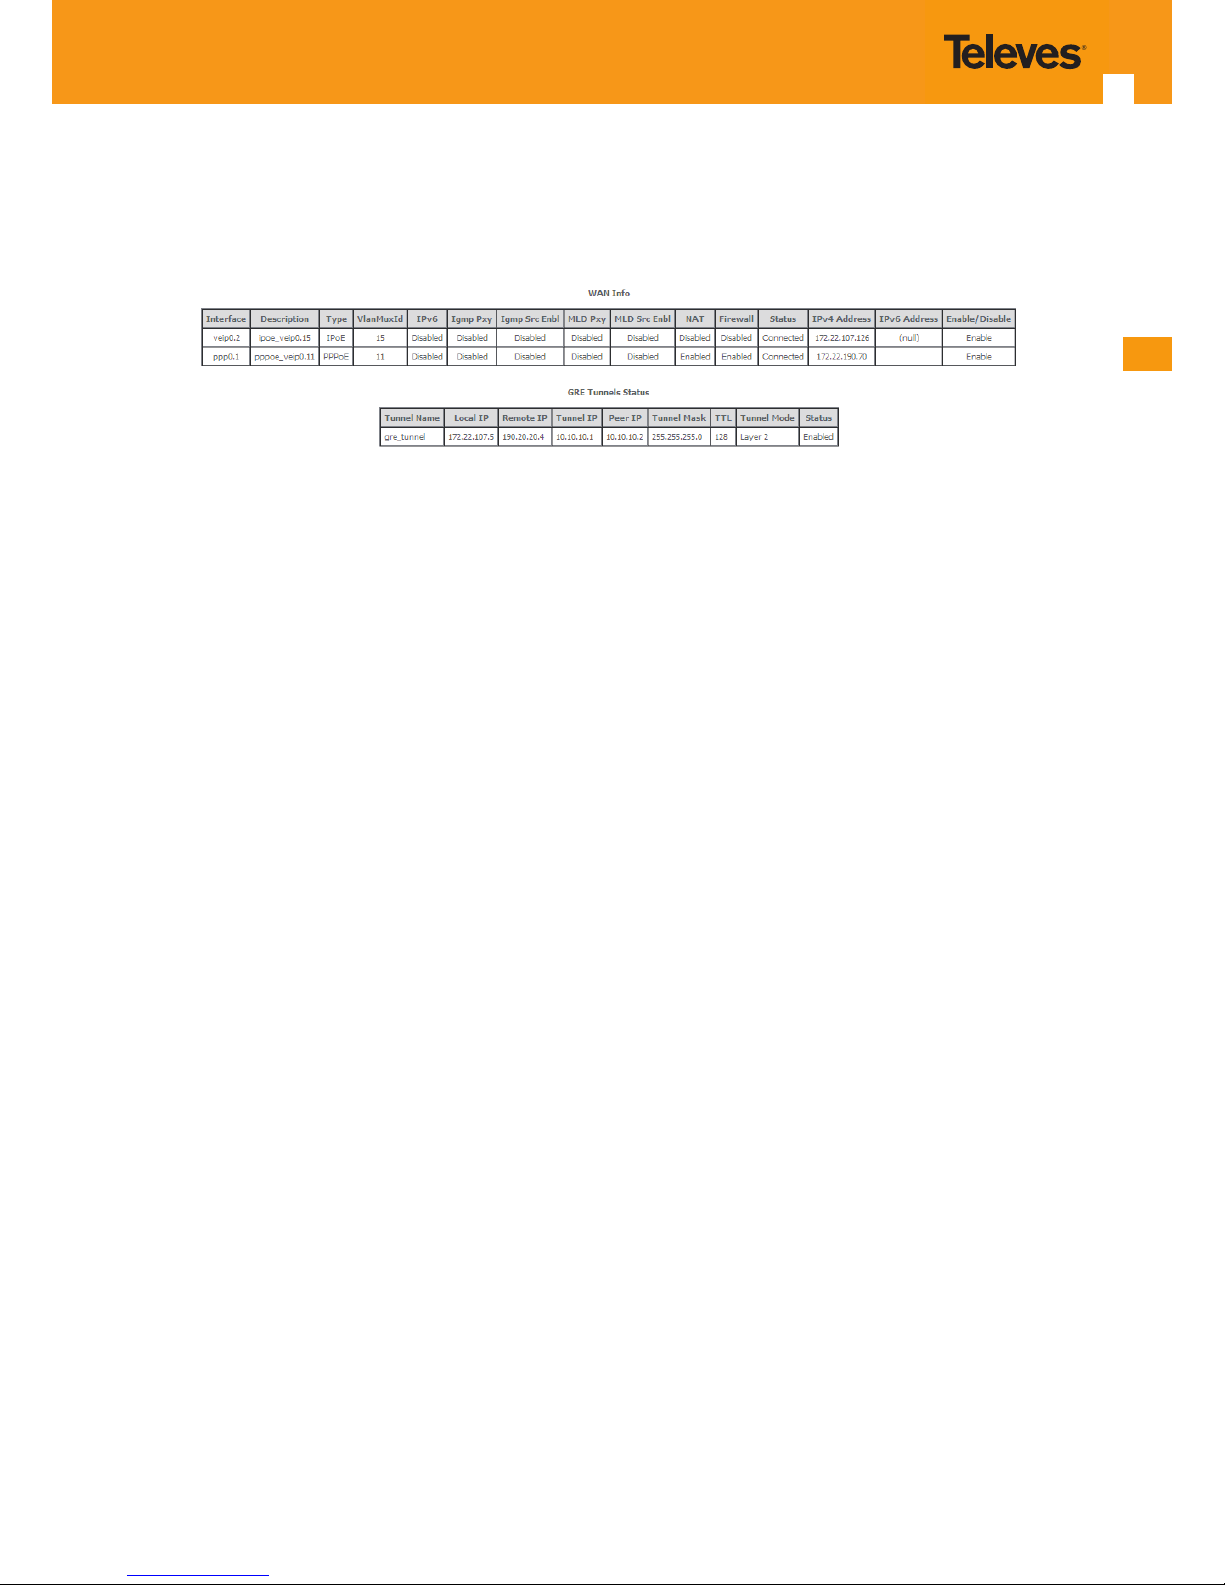
EN
73
It is now possible to view the currently congured WAN services’ parameters as well as obtained IP addresses by Selecting the Device Info sub-
menu item WAN, Figure 5-63.
Figure 5-63:Device Info- WAN Service Current conguration
5.6.2.3.3 Interface Grouping for GRE
After the GRE tunnel creation, association between the WAN and the desired interfaces must be done.
At the Advanced Setup menu the item Interface Grouping must be selected. An Interface Grouping Conguration window will be displayed.
An on-line help on interface grouping is available at the conguration window:
STEP 1. Name the interfaces group, Figure 5-64, 1;
STEP 2. At the Wan interface used in the group selection combo box, select the wan interface for the grouping, in this case the GRE previ-
ously congured interfaces, Figure 5-64, 2 and Figure 5-67 To nalize the conguration use the Save/Apply button, Figure 5-65-6.
The next displayed window is initial window, the Advanced Setup- Interface grouping initial window where the newly congured
group, brgre in this example, Figure 5-67;
STEP 3. Figure 5-64; From the list of available WAN interfaces select the desired wan interface, in this example wlan0, Figure 5-66-3;
STEP 4. Click on the left pointing arrow, Figure 5-66-4, to move the selected interface (wlan0 in this example) from the Available LAN Inter-
faces List to the Grouped LAN Interfaces, Figure 5-65-5;
STEP 5. Wlan0, the selected interface for interface grouping is now show at the grouped LAN interfaces list, Figure 5-65-5;
STEP 6. To nalize the conguration use the Save/Apply button, Figure 5-65-6. The next displayed window is initial window, the Advanced
Setup- Interface grouping initial window where the newly congured group, brgre in this example, Figure 5-67.
Page 74
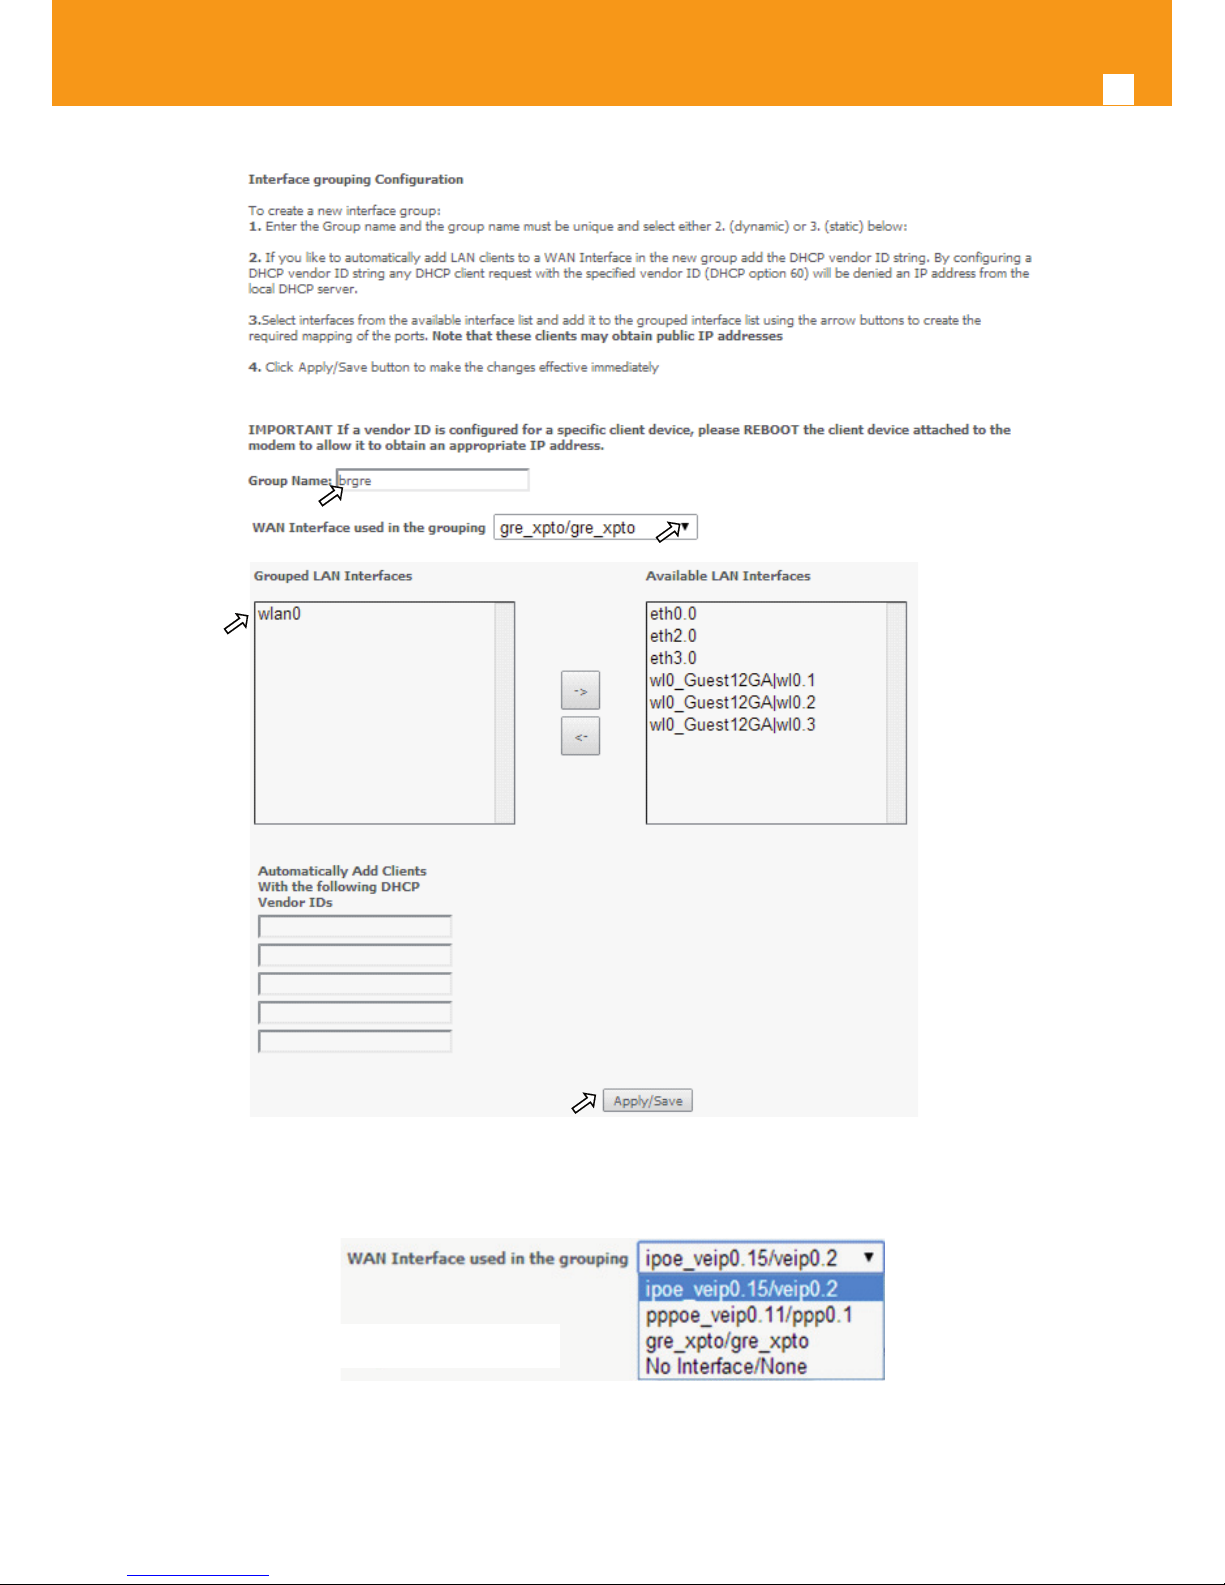
74
GPON ONT
1
2
5
6
Figure 5-64: Advanced Setup- interface grouping conguration window
Figure 5-65: Wan interface used in the grouping selection combo box
Page 75
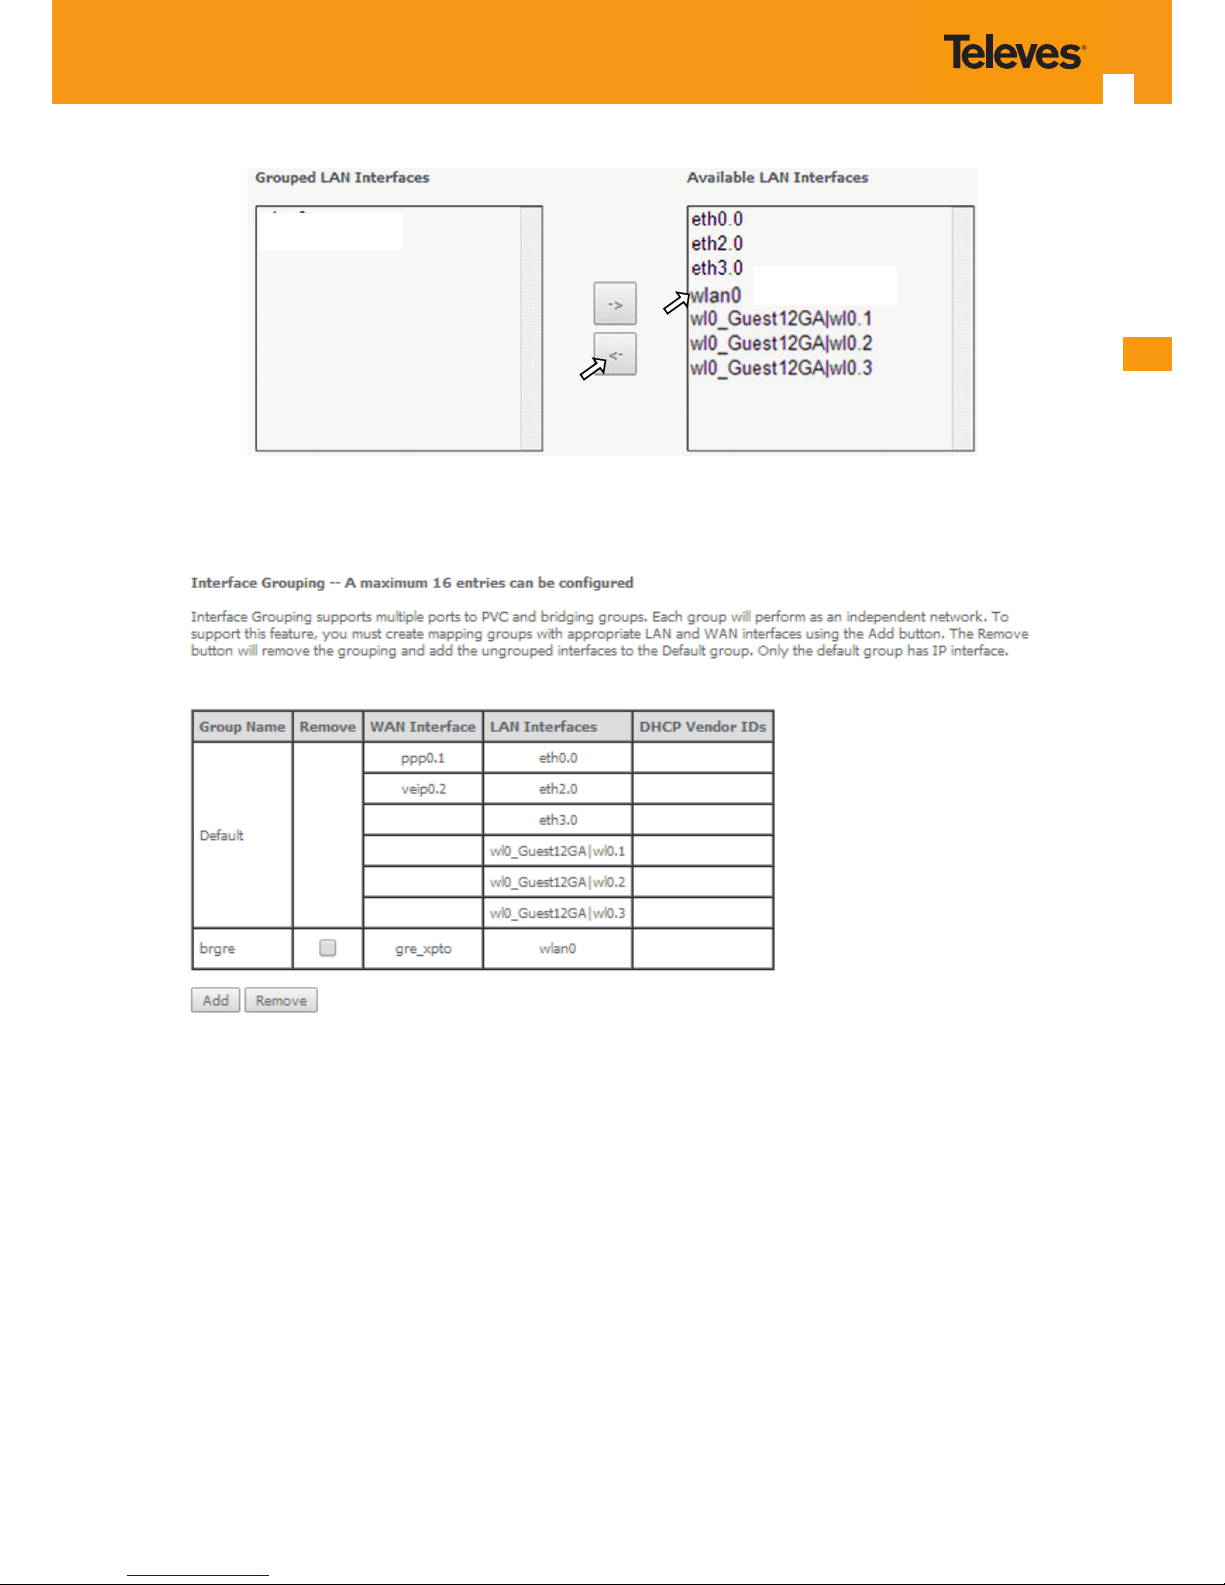
EN
75
3
4
Figure 5-66: Advanced Setup- interface grouping conguration window
Figure 5-67: Advanced Setup- Interface grouping conguration initial Window: Current interface grouping conguration
Page 76
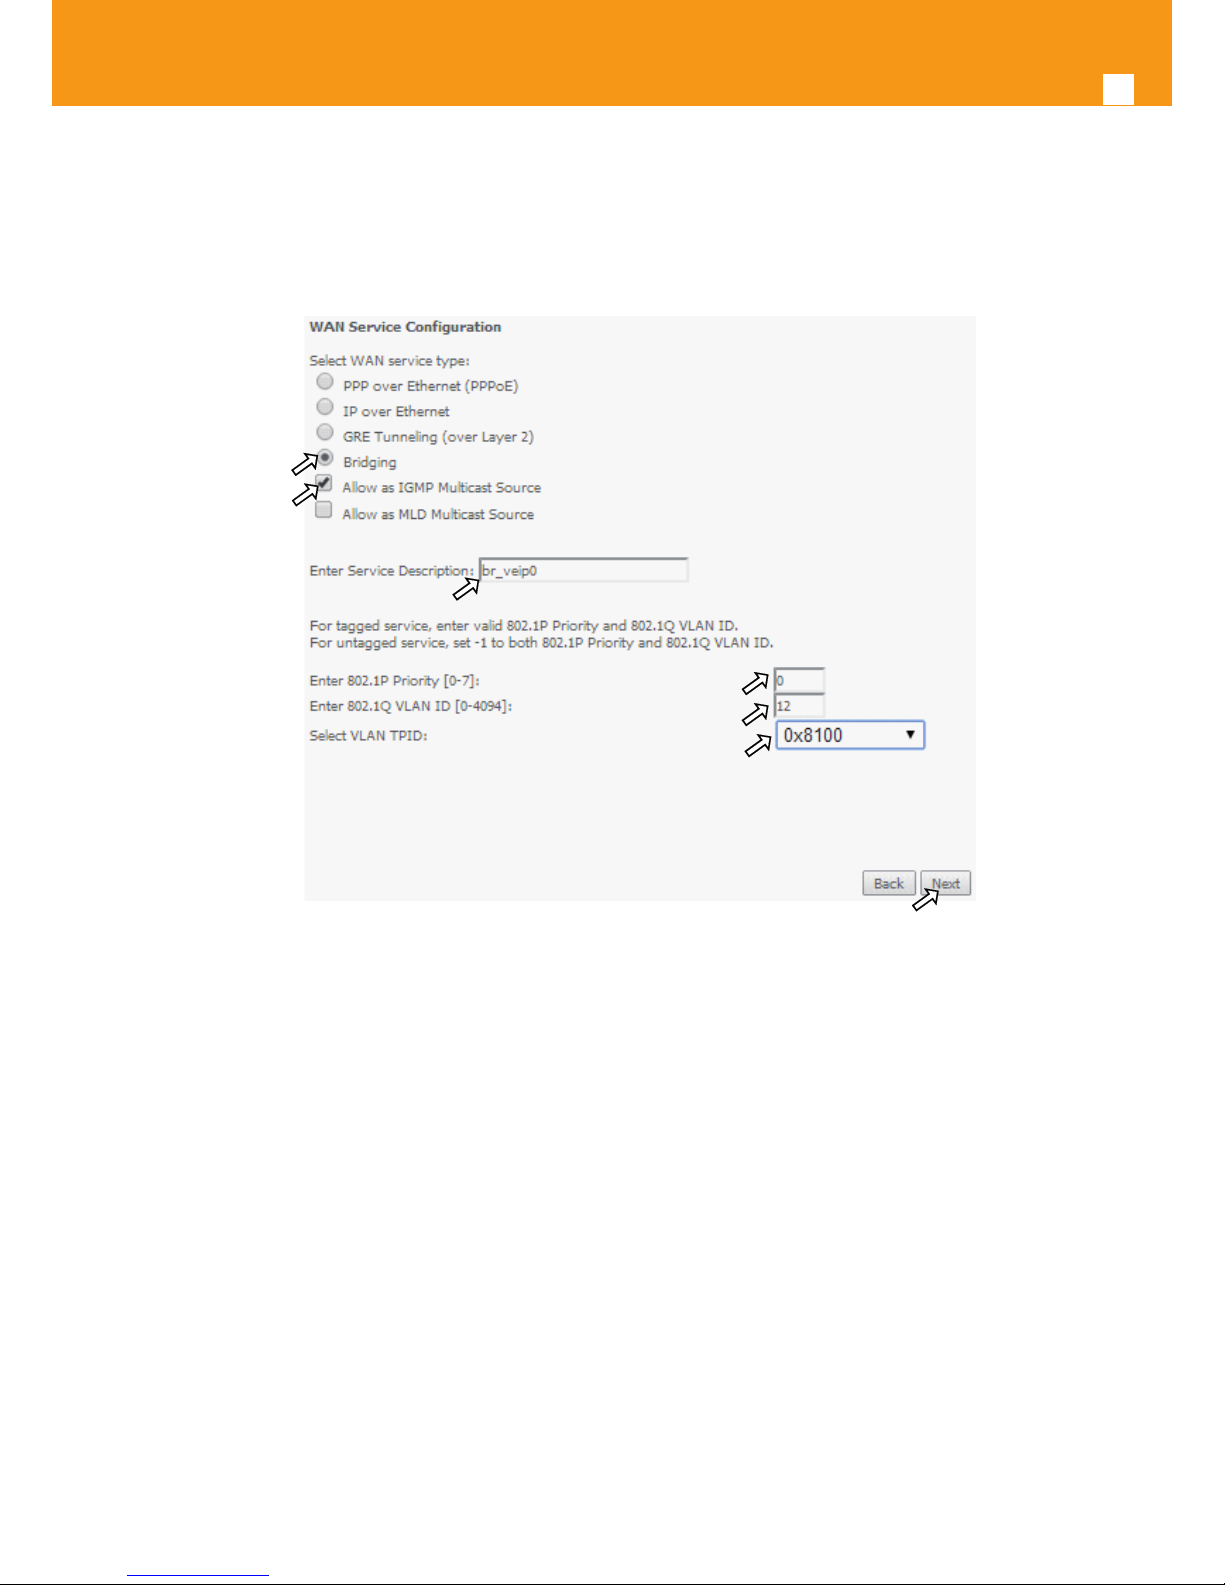
76
GPON ONT
5.6.2.4 Bridging Service Conguration
After the selection of the WAN interface associated to the service to create, Figure 5-21 and Figure 5-22 , use the Next button at Figure 5-22, to
progress to the next WAN Service setup window- Wan service Conguration, gure 5-68.
1
3
4
5
6
7
2
Figure 5-68: WAN service setup – type of service selection and service conguration – Bridging service
At this window execute the following steps:
STEP 1. Select the Bridging WAN service type, Figure 5-68-1;
Multicast source options are displayed for selection: IGMP or MLD
STEP 2. Select which multicast source protocol to use, if any, (IGMP or MLD) Figure 5-68-2;
STEP 3. At the Field Service Description enter a string for the service description ; the default service description is a string automatically
lled in when the type o device is selected(Step1) and composed by the type of Service followed by underscore and the WAN interface name , e.g. br_veip0, Figure 5-68-3;
STEP 4. For tagged service, at the eld 802.1P priority, enter the pbit value (0-7) to mark the upstream trac according to the desired CoS
for the service to create; a higher value corresponds to a higher priority CoS, Figure 5-68-4;
For untagged service leave the led with the default value of -1;
STEP 5. For tagged service, at the VLAN ID eld enter the VLAN ID value (0-4094) of the VLAN used by the service, , Figure 5-68-5
For untagged service leave the eld with the default value of -1;
STEP 6. For tagged service select a TPID value from the selection combo box, , Figure 5-68-6.
Page 77
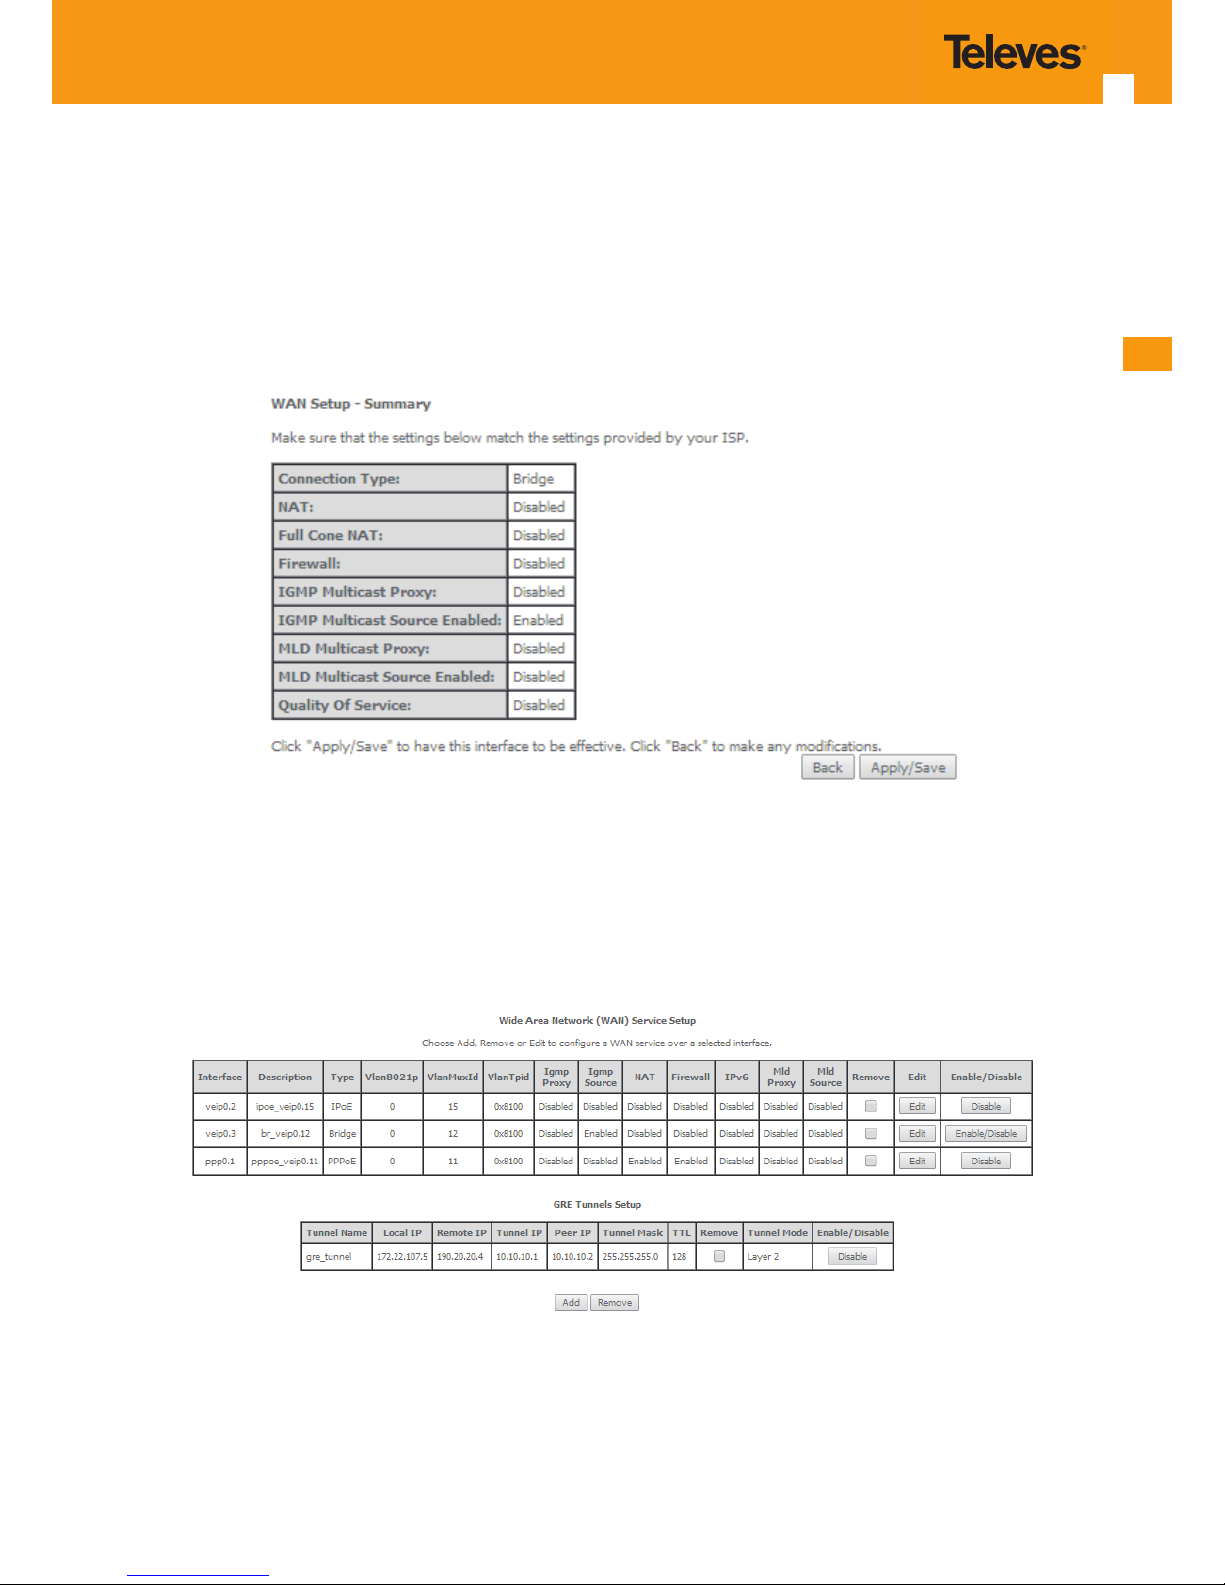
EN
77
0x8100, TPID default value; if selected a single tagged service is congured
0x88A8 or 0x9100, TPID used for the outer VLAN (S-VLAN) for double tagged services; if selected a double VLAN tagged service is
congured; in this case the inner VLAN (C-VLAN) tag TPID has the default value of 0x8100;
STEP 7. Once the WAN service setup parameters are congure use Next button, , Figure 5-68-7 on to progress to the WAN Service Setup Sum-
mary window, Figure 87. This table should eect the conguration for the WAN service setup parameters than have been entered.
Please verify the presented conguration match the settings provided by the ISP for this service.
Figure 5-69: WAN Service Setup Summary window
To nalize the conguration use the Save/Apply button, Figure 5-69. The next displayed window is initial window, the WAN Service Window, where
the service congured is displayed in the corresponding table, Figure 5-70.
Figure 5-70: WAN Service Setup Initial Window- service conguration displayed
It is now possible to view the congured WAN service parameters by Selecting the Device Info sub-menu item WAN, Figure 5-71.
Page 78
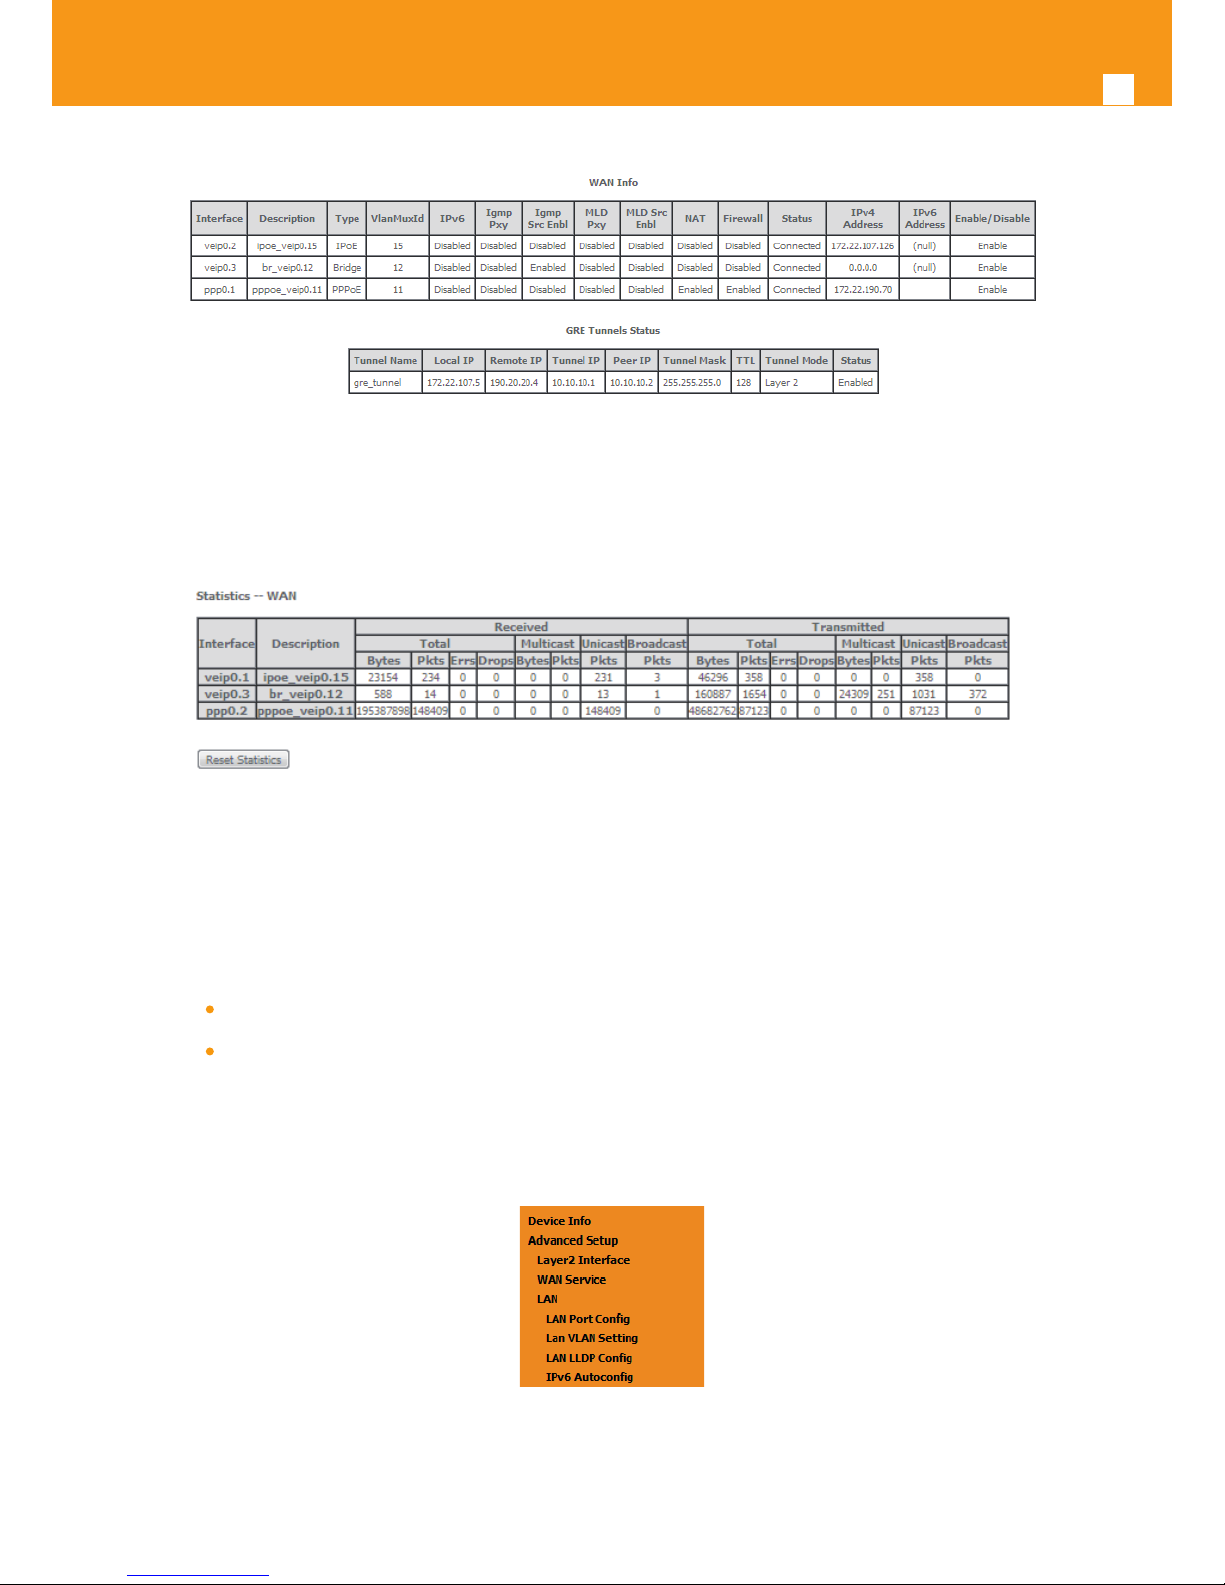
78
GPON ONT
Figure 5-71: Device Info- WAN Service Current conguration and IP Address
Service statistics can be obtained by selecting at the menu Device Info the submenu Statistics, item Wan; a Services-WAN statistics window will
be displayed, Figure 5-72. Please refer to Table 5-5 for the description of the statistics window displayer parameters.
Figure 5-72: Device Info/Statistics/WAN-- WAN Services Statistics Information
5.6.3 LAN
Selection of Advanced Setup submenu item LAN will display a LAN submenu with two items, Figure 5-73:
Lan VLAN Setting
IPv6 Autocong
In the main window a Local Area Network (LAN) Setup window is displayed, Figure 5-74.
This window allows the conguration Multicast, rewall and DHCP in the LAN.
Figure 5-73: Advanced Setup LAN Sub-menu
Page 79
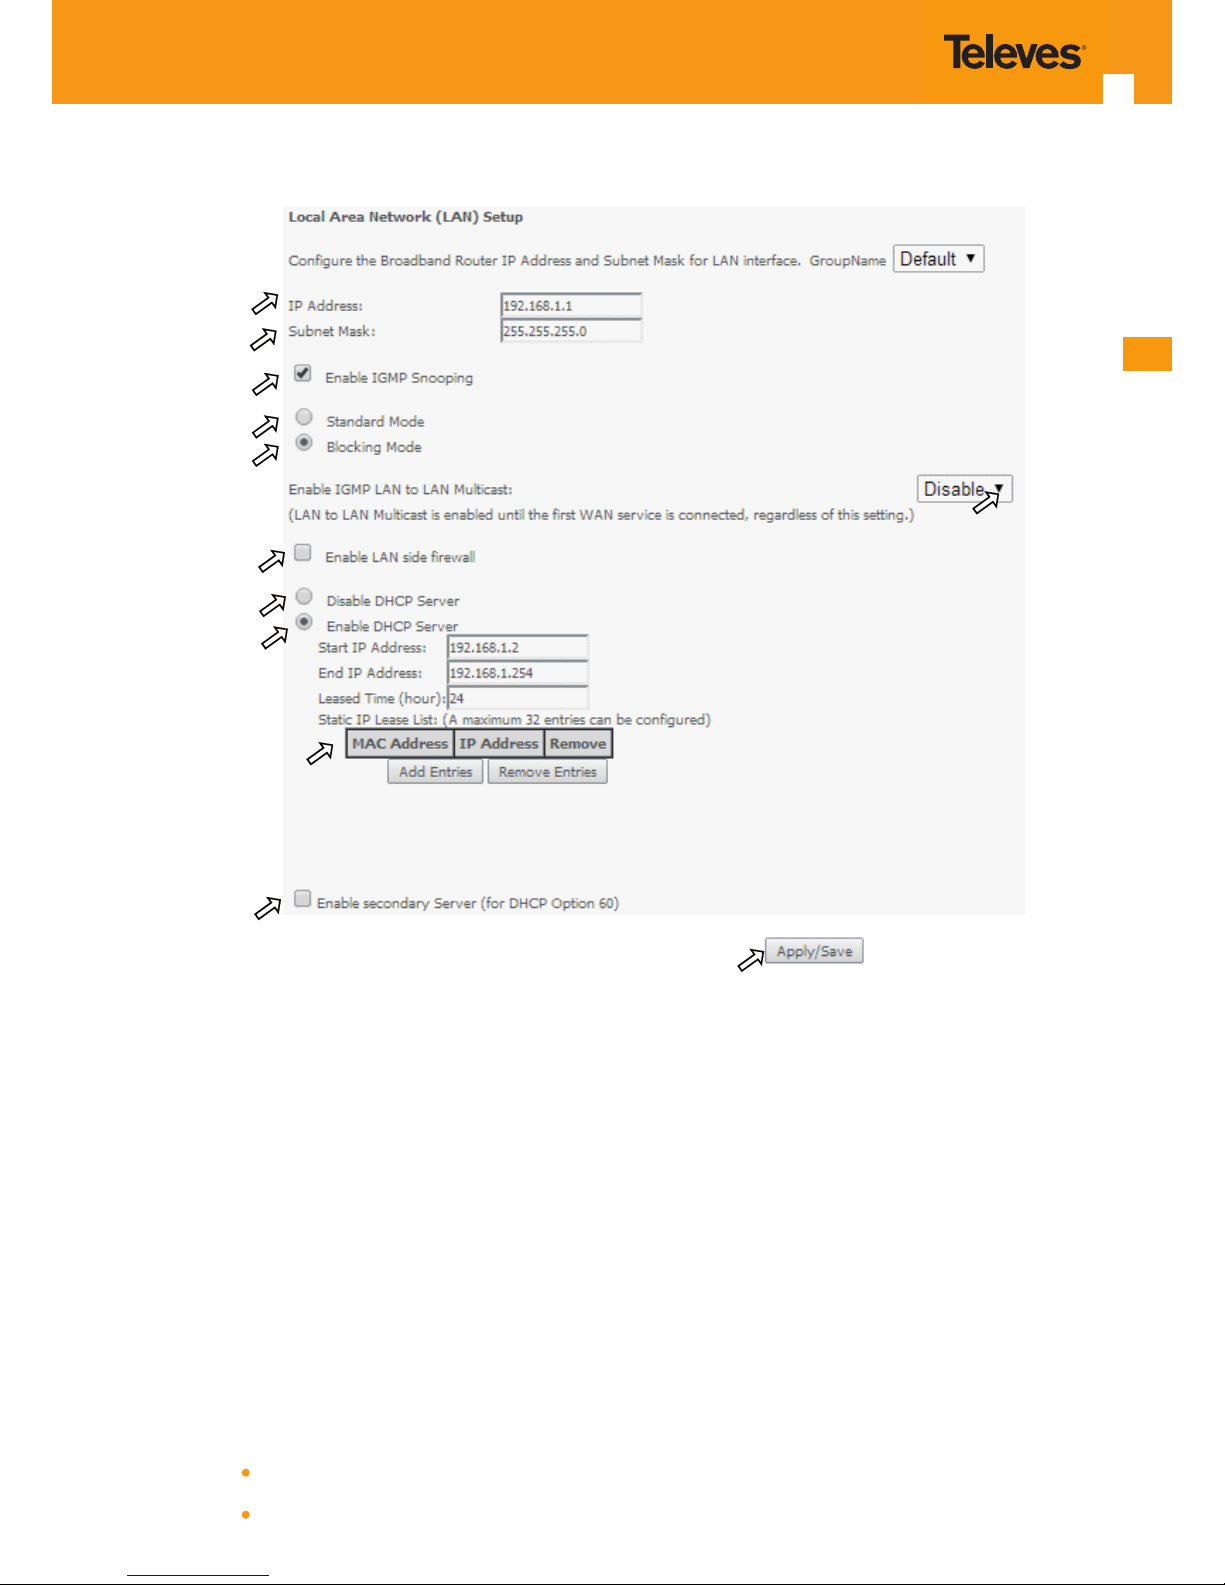
EN
79
1
2
3
4
5
6
7
8
9
10
11
12
Figure 5-74: Advanced Setup - LAN Setup window
At this window execute the following steps:
STEP 1. IP Address –This is the Refs. 769501-769502 IP Address, default value 192.168.1.1, Figure 5-74-1;
STEP 2. Refs. 769501-769502 sub network Mask ; default value is 255.255.255.0, Figure 5-74-2;
STEP 3. In order to enable IGMP Snooping select this option, Figure 5-74-2;
In the case IGMP snooping is not selected multicast packets are send to all bridge ports. If this option is selected an IGMP
Snooping mode must be selected (see step 4 and step 5)
There are two modes of IGMP snooping, that establish the way groups multicast packets are forwarded by the bridge Figure 5-74- 4 and 5:
STEP 4. Standard Mode, Figure 5-74-4,
Group multicast packets are forwarded to all ports if there was no previous IGMP Group report by any port:
In the case there were previous IGMP Group reports, multicast packets are only forwarded to the ports that previously send
Page 80
80
GPON ONT
IGMP group reports.
STEP 5. Blocking mode, Figure 5-74 , 5.
In this mode multicast packets are only forwarded if there were previus IGMP reports, for the ports that send these reports.
Packets are not forwarded if there were no IGMP reports
STEP 6. In order to have a multicast data source on LAN side and IGMP snooping enabled, then LAN-2-LAN multicast option must be en-
abled, Figure 5-74-6;
LAN-2-LAN multicast is enabled (even if this option is set to disable) until the rst WAN service is connected.
STEP 7. This option must be selected in order to enable LAN side rewall; if LAN side rewall is enabled, Figure 5-74-7,
STEP 8. If selected Refs. 769501-769502 DHCP server is disabled, Figure 5-74-8;
STEP 9. If selected Refs. 769501-769502 DHCP server is enabled, Figure 5-74-9; the pool of IP address to use must be dened by indicating:
start IP address; default value is 192.168.1.2
end IP addresses; default value is 192.168.1.254
Leased Time: amount of time (in hours) then the LAN user will be allowed the dynamic IP address that has been allocated
to him; default value is 24.
Static IP lease settings allow the reservation of static IPs for PCs in the LAN that will therefore obtain the same static IP address each time they
request an IP address from the Refs. 769501-769502 DHCP server . For the Refs. 769501-769502 DHCP Server up to 32 Static IP leases can be
congured
STEP 10. To congure static IP leases, Figure 5-74-10, use the Add entries button ;
Each entry will consists f a MAC address of the PC to which the static IP address will be reserved and the Static IP reserved for
this PC; enter the MAC address and the reserved IP address for this MAC.
STEP 11. If Option “Enable secondary Sever (for DHCP option 60)” is selected, Figure 5-75, elds requesting information for conguration of
this option will be shown (DHCP option 60 is vendor ID);Enabling this option allows to add LAN clients on a WAN interface requesting DHCP with option 60
IP Address: DHCP Server ( Refs. 769501-769502) IP Address;
Subnet Mask: Refs. 769501-769502 sub network Mask ; default value is 255.255.255.0;
Start IP address: First IP address to use by DHCP server for allocation;
End IP addresses: Last IP address to use by DHCP server for allocation;
Leased Time: amount of time (in minutes) then the LAN user will be allowed the dynamic IP address that has been allocated to him;
Vendor ID: String identier for vendor ID (DHCP option 60);
Primary DNS Server: Primary DNS Server IP address;
Secondary DNS server: Secondary DNS Server IP address;
NTP server: NTP server IP Address
TFTP Server: TFTP Server IP Address
Page 81
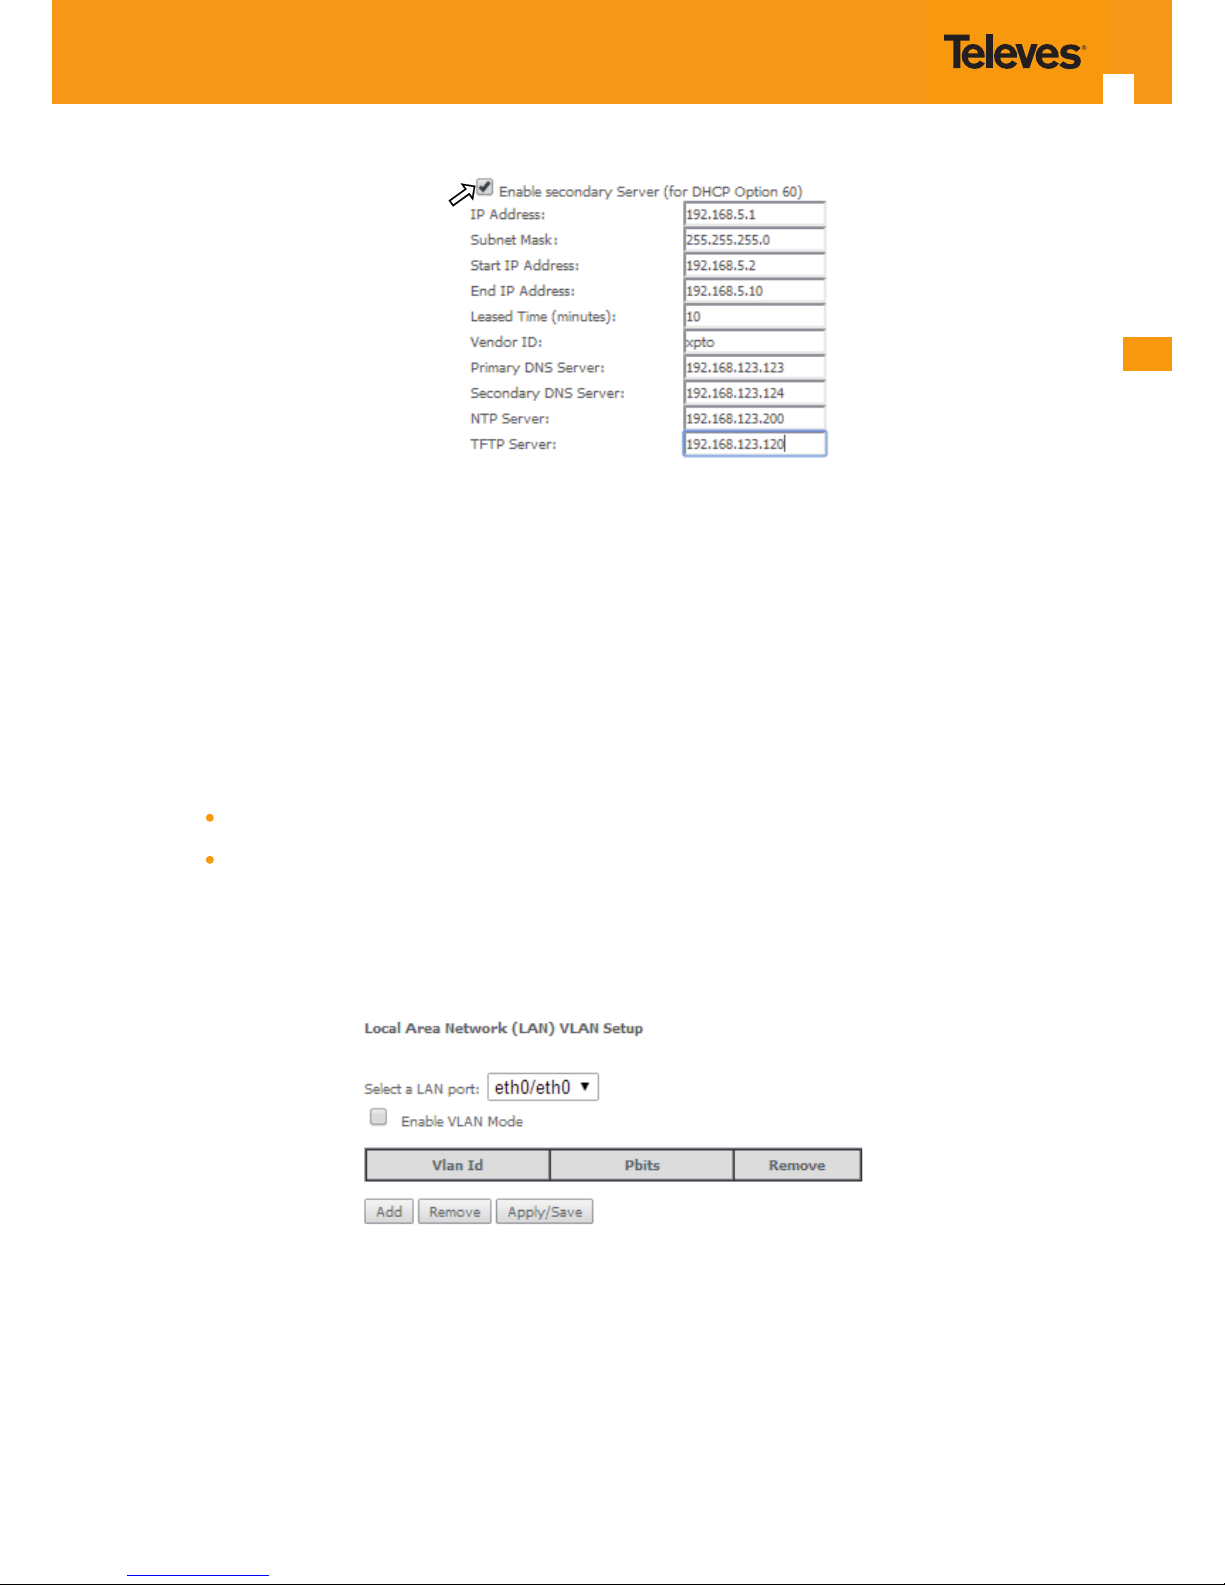
EN
81
11
Figure 5-75: Advanced Setup - LAN Setup window- Enable Secondary server (for DHCP Option 60)
STEP 12. To nalize the conguration use the Save/Apply button, Figure 5-74, -12; the displayed window will show the LAN settings cur-
rent conguration
5.6.3.1 LAN VLAN Settings
Selection of Advanced Setup submenu LAN, item will Lan VLAN Setting a Local Area Network (LAN) VLAN Setup window is displayed in the main
window Figure 5-74.
In order to create Lan VLANs, a LAN port must be chosen at the Selection combo box, Figure 5-76.
To create a Lan VLAN use the Add button and at the table entry created, Figure 5-77, ype in the:
VLAN Id : Species the VLAN identier; values from 0 to 4096;
Pbits: assigned priority value (0-7).
To nalize the conguration use the Save/Apply button, Figure 5-77; the displayed window will show the LAN settings current conguration.
Figure 5-76: Advanced Setup –LAN/ Lan VLAN setup window
Page 82
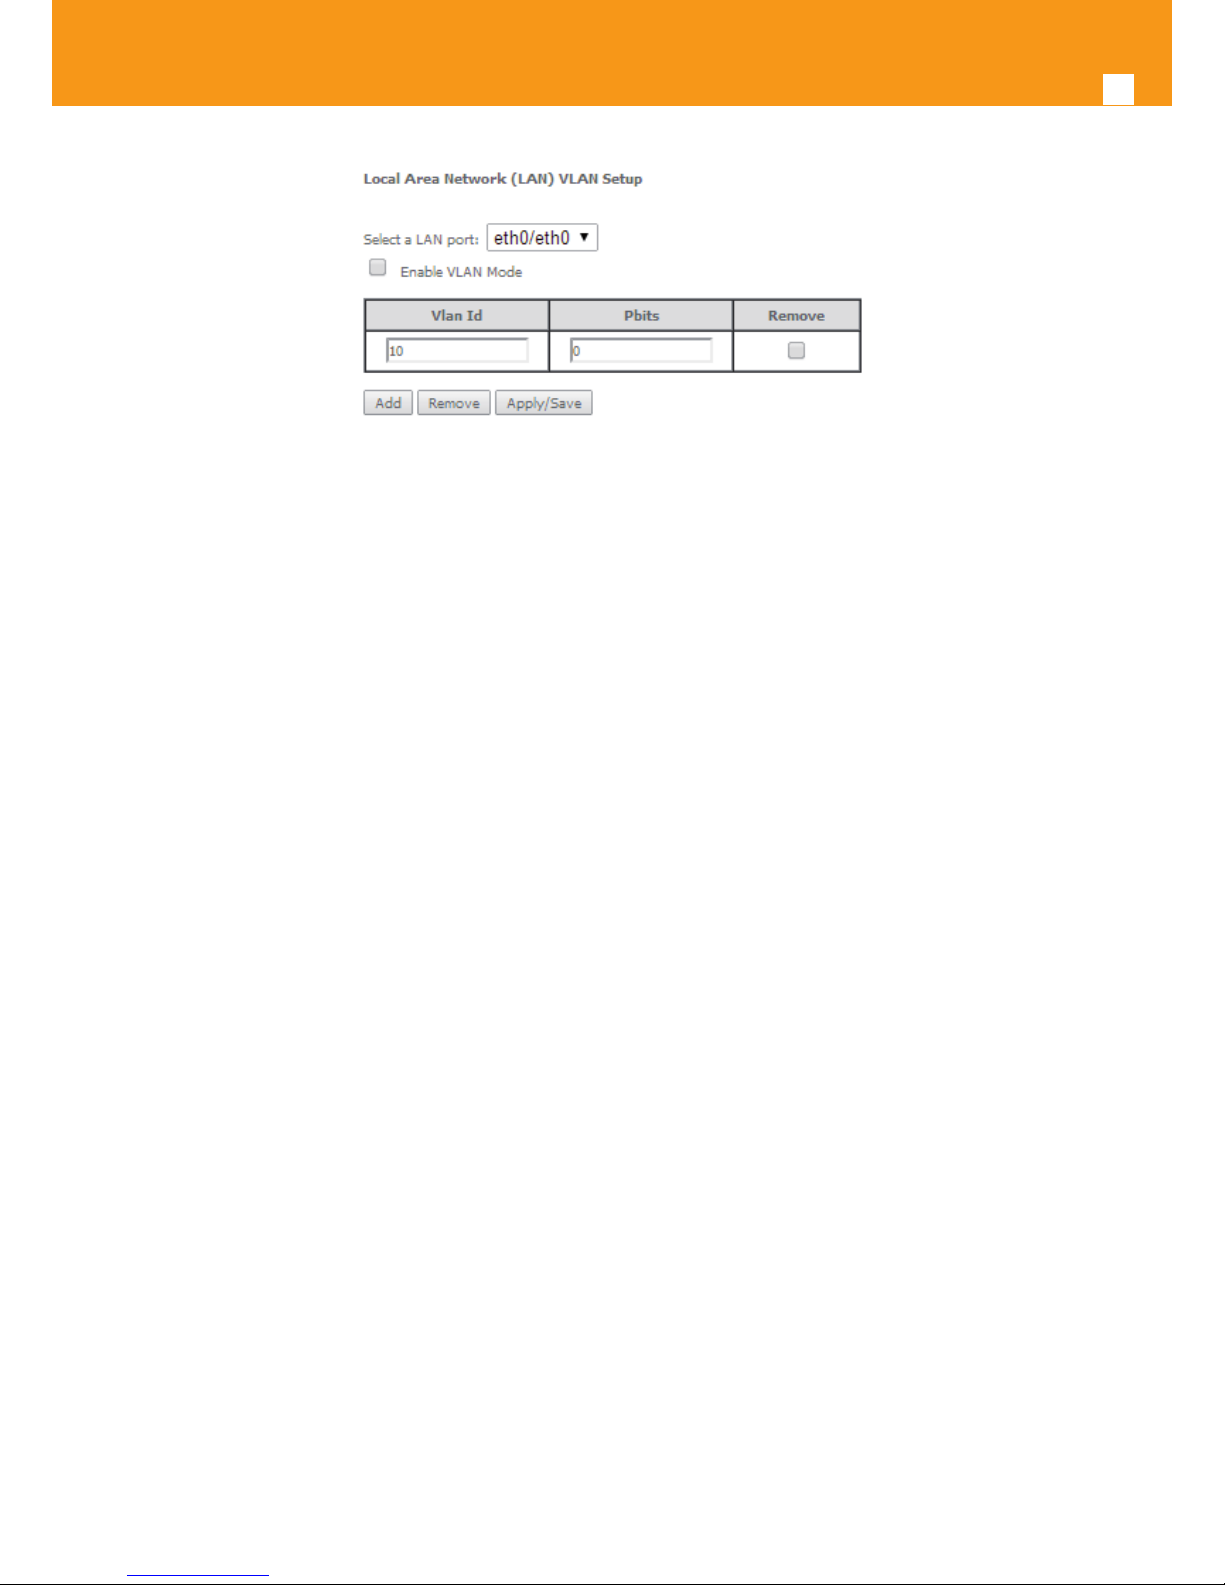
82
GPON ONT
Figure 5-77: Advanced Setup –LAN/ Lan VLAN setup window- Add and congure a Lan VLAN
Lan VLAN can be congured in advance as described before and not enabled. To Enable Lan VLAN afterwards, option “Enable VLAN Mode” must
be selected, and then the Save/Apply button used to nalize the conguration.
5.6.3.2 IPv6 Autocong
Selection of Advanced Setup submenu LAN, item will IPv6 Autocong an IPv6 VLAN Auto Conguration window is displayed in the main window
Figure 5-78. A short on line help text is provided in the conguration window.
For a typical IPv6 VAN Auto Conguration setting, shown in Figure 5-78, execute the following Steps, Figure 5-78:
STEP 1. Select Option “Enable DHCPv6 Server;
STEP 2. Selectthe option “Stateless”;
STEP 3. Select the option “Enable RADVD”;
STEP 4. Select the option “MLD Snooping”;
STEP 5. Select the option “Blocking Mode”;
STEP 6. To nalize the conguration use the Save/Apply button
Page 83
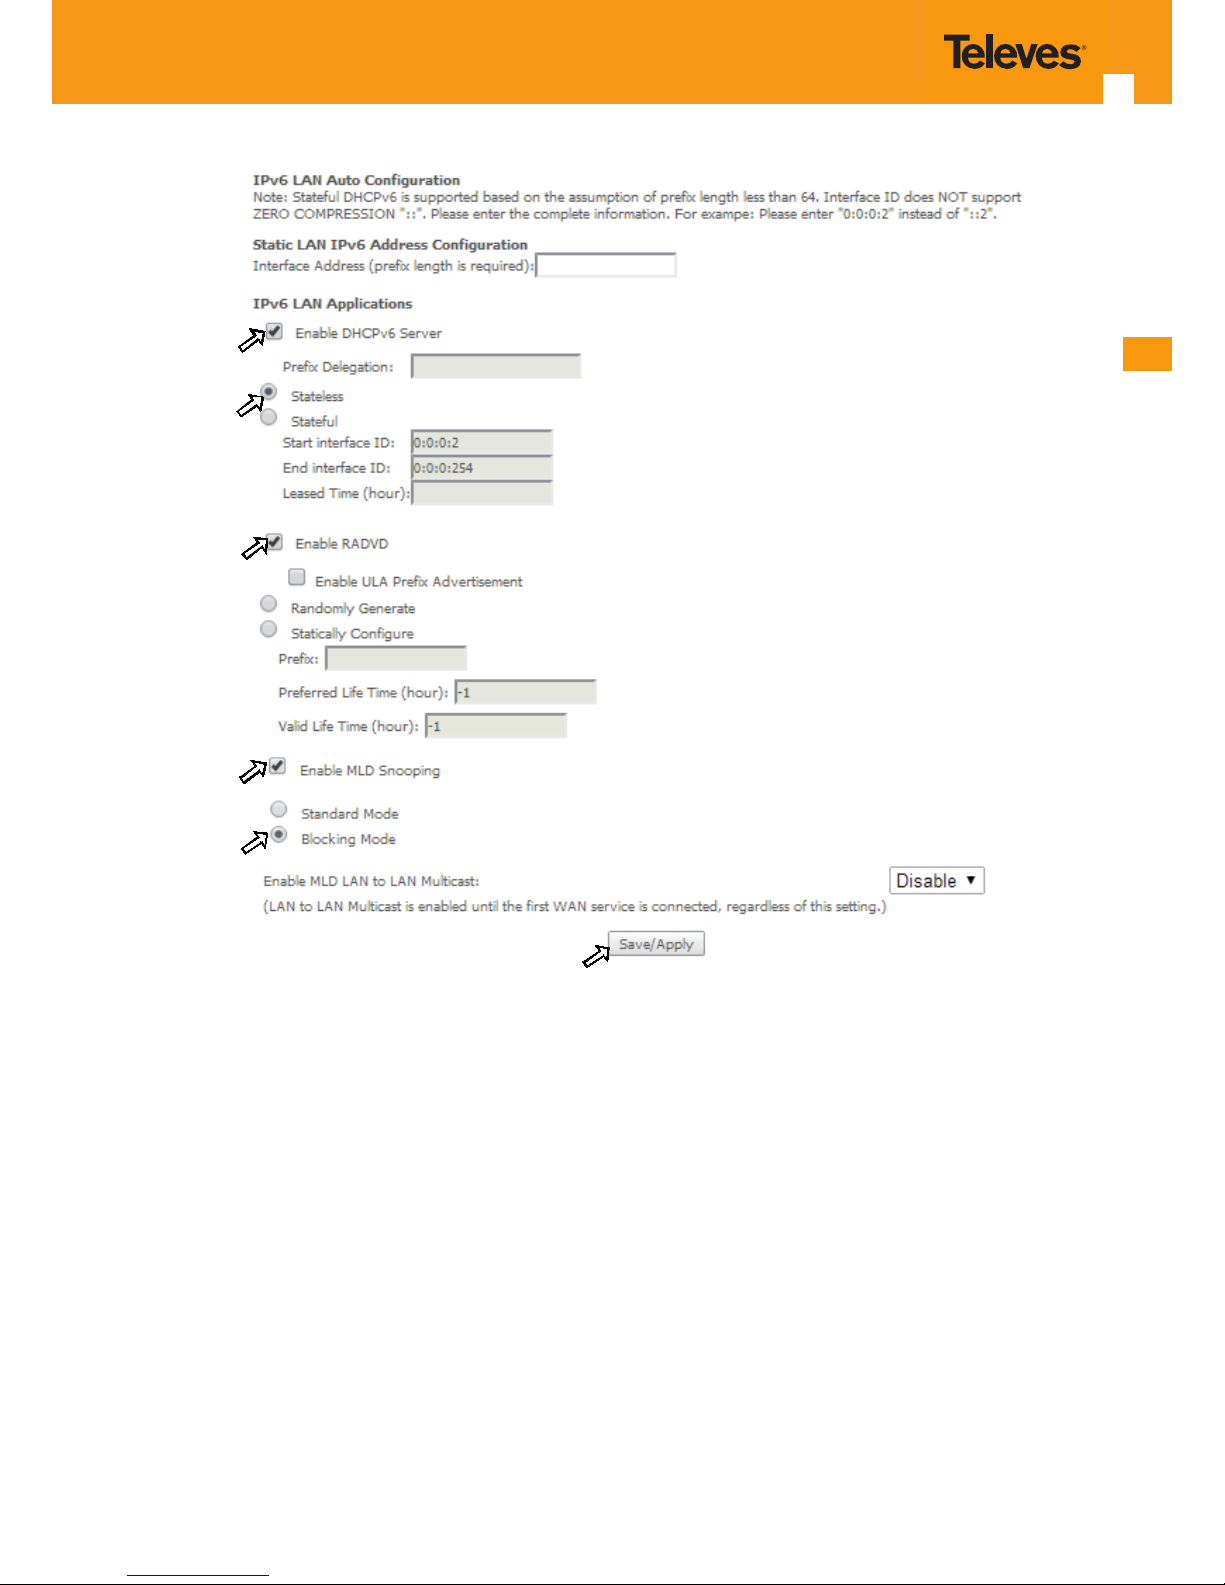
EN
83
1
2
3
4
5
6
Figure 5-78: Advanced Setup –LAN/ IPv6 VLAN Auto Conguration window
Page 84
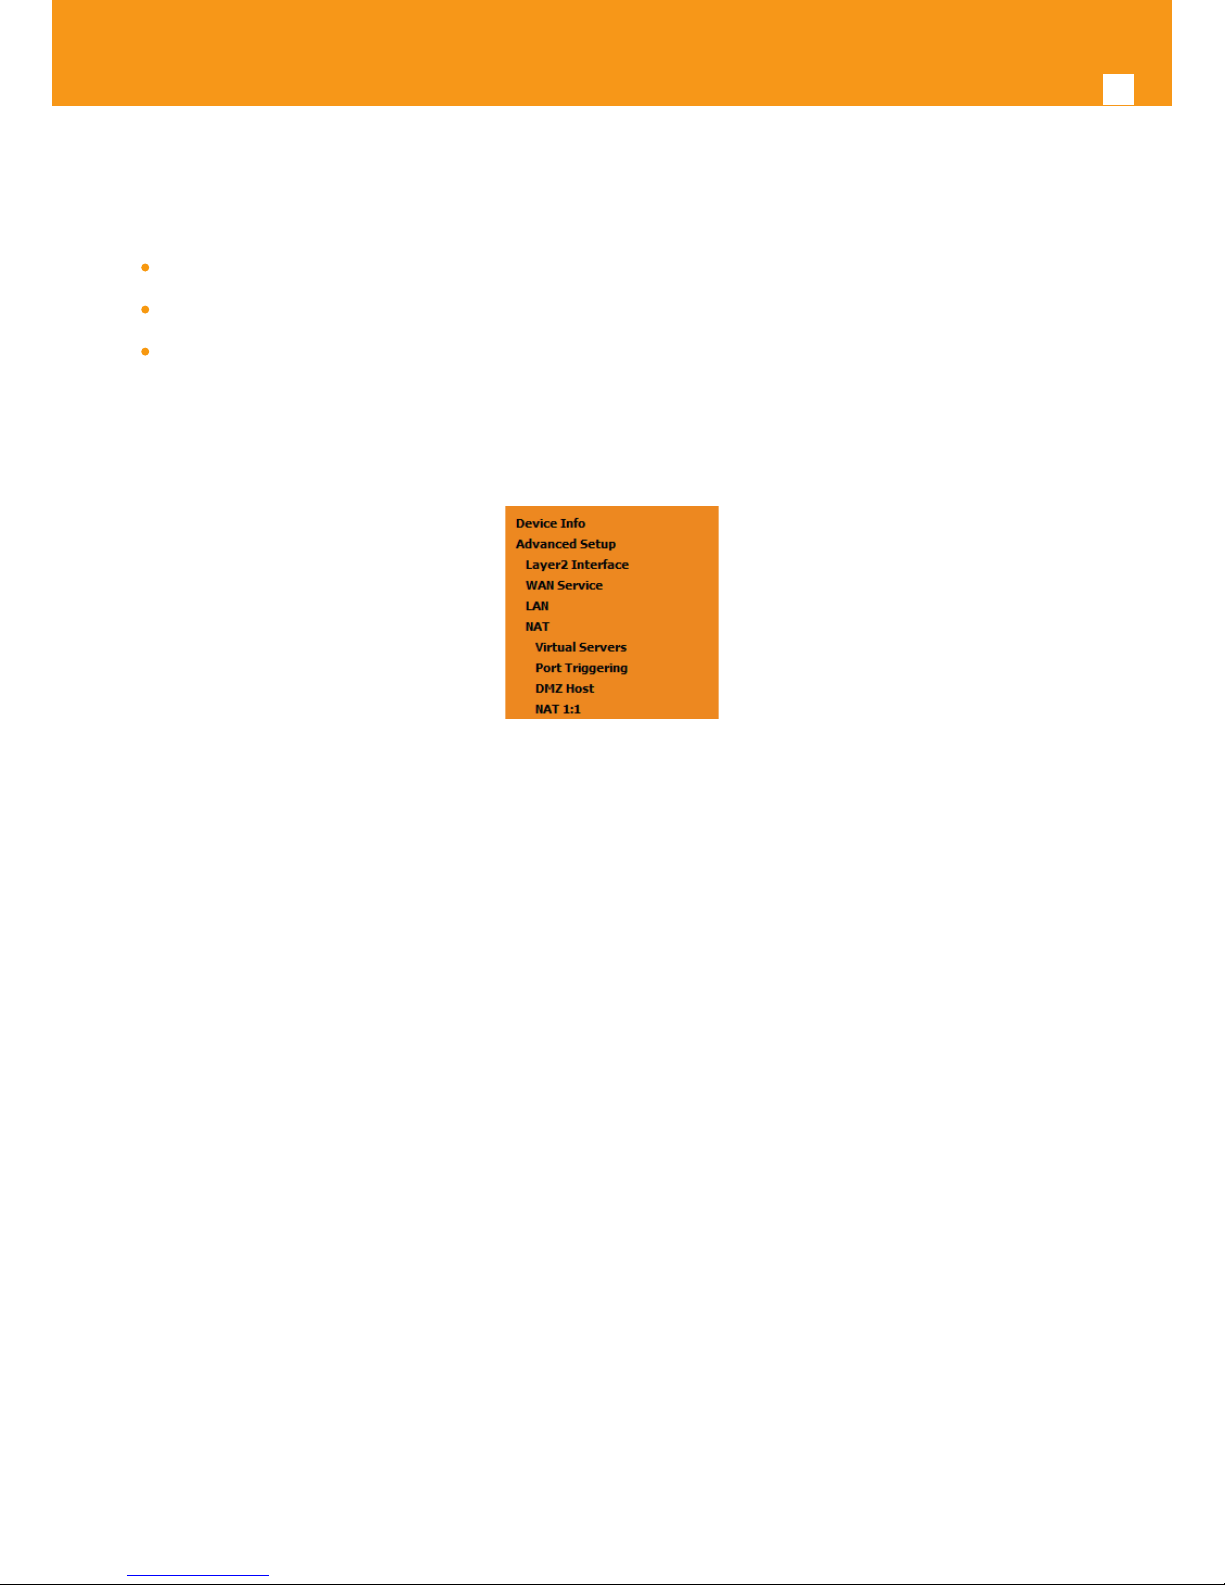
84
GPON ONT
5.6.4 NAT
Selection of Advanced Setup submenu item NAT will display a NAT submenu with three items, Figure 5-79:
Virtual Servers
Port Triggering
DMZ Host
In the main window a NAT-Virtual Servers Setup window is displayed, Figure 5-80, showing the current NAT-Virtual servers conguration.
Figure 5-79: Advanced Setup NAT Sub-menu
5.6.4.1 Virtual Servers
Selection of Advanced Setup submenu NAT, item Virtual Servers a NAT-Virtual Servers Setup window is displayed in the main window Figure 5-80,
showing the current NAT-Virtual servers conguration.
This window allows inserting and conguring port forwarding, redirecting a network port from one network mode to another network mode. This
allows a user from the WAN side of the network to reach a PC on the LAN side of the network for which ports were opened. The WAN interface used
must have NAT enabled. A short on line help text is provided in the conguration window.
To insert and congure a new NAT-Virtual server use the Add Button, Figure 5-80; a new window is displayed, Figure 5-81, allowing the conguration of a new Nat- virtual Server entry, Figure 5-82. A short on line help text is provided in the conguration window.
The rst part of the conguration consists on choosing the Wan interface, the Service name and the server IP address.
To save and apply this conguration, use the Apply/Save button, Figure 5-81-1. The port forwarding table will be updated with the chosen service
predened port forwarding conguration, Figure 5-81.
To nalize the conguration use the Apply/Save button below the table, Figure 5-81-2. The next displayed window is the initial window, showing
the current NAT - virtual servers’ conguration, Figure 5-83.
Page 85
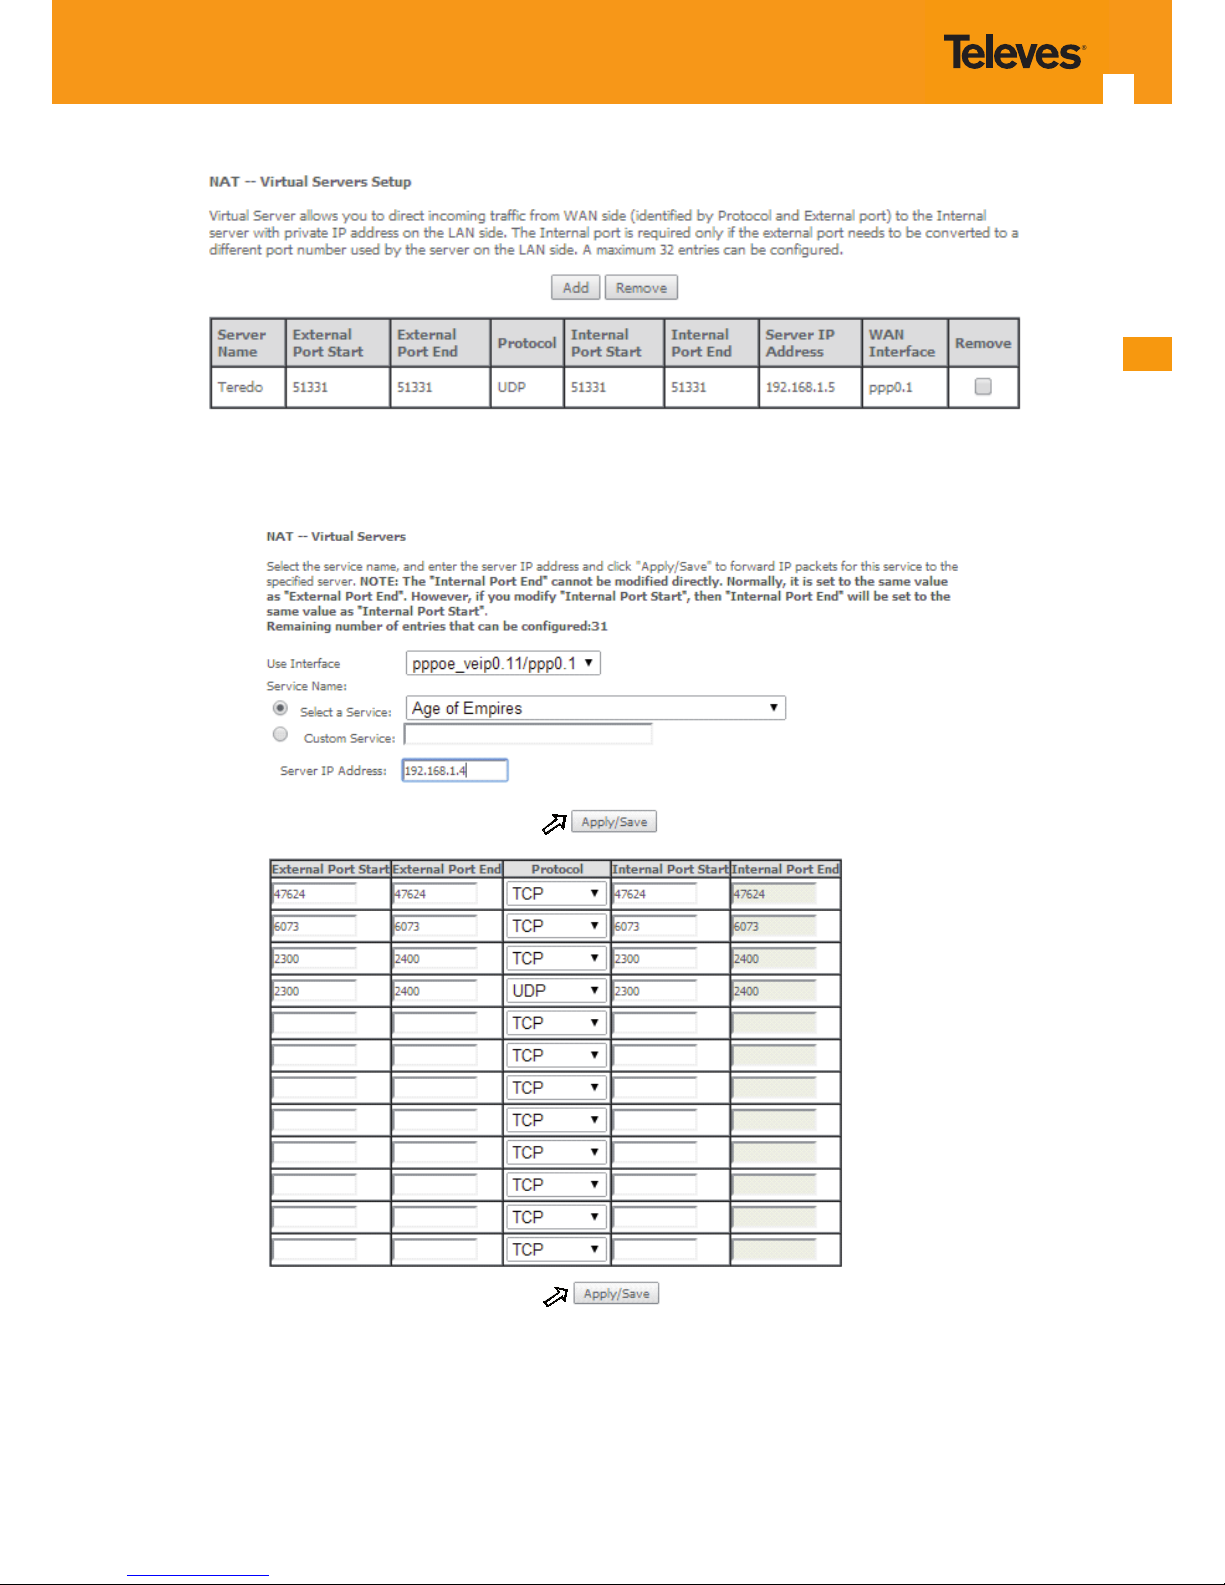
EN
85
Figure 5-80: Advanced Setup/NAT-Virtual Servers Setup window
1
2
Figure 5-81: Advanced Setup/NAT-Virtual Servers Setup window - Wan port, Service and Server IP Address Conguration
Page 86
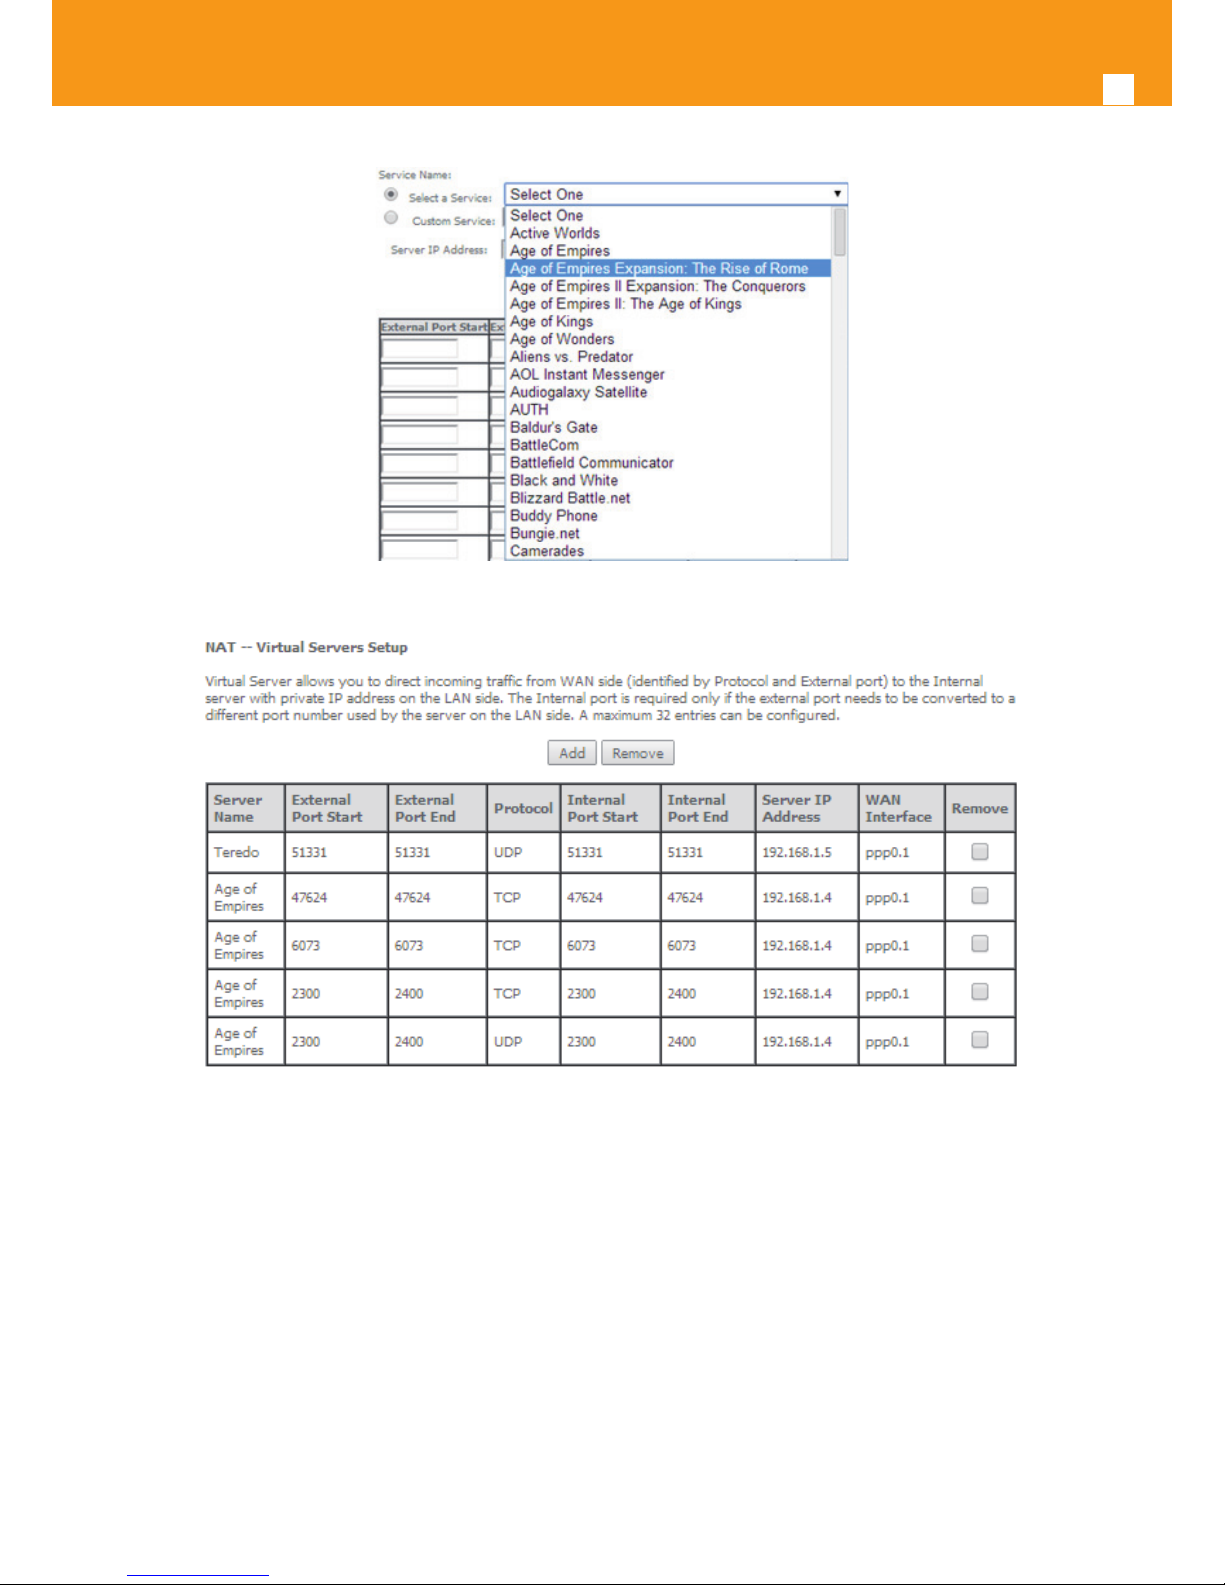
86
GPON ONT
Figure 5-82: Advanced Setup/NAT-Virtual Servers Setup window - Service Selection Combo box
Figure 5-83: Advanced Setup/NAT-Virtual Servers Setup window - Current NAT Virtual Server Conguration
5.6.4.2 Port Triggering
Selection of Advanced Setup submenu NAT, item Port Triggering, a NAT-Port Triggering Setup window is displayed in the main window Figure
5-84, showing the current NAT- Port Triggering conguration. A short on line help text is provided in the setup window.
This window allows inserting and conguring port triggering, for dened applications. This redirects a network port from one network mode to
another network mode. This conguration allows opening ports of a PC in the LAN for a user on the WAN side only when the session on the Lan
side is active- this is always initiated by the PC in the network LAN side, being safer then port forwarding.
To insert and congure a new NAT-Port Triggering entry use the Add Button, Figure 5-84; a new window is displayed, Figure 5-85. A short on line
help text is provided in the conguration window.
This window allows the conguration of Port Triggering by choosing the Wan interface and the Application Name, Figure 5-85. The WAN interface
to use must have NAT enabled.
Page 87
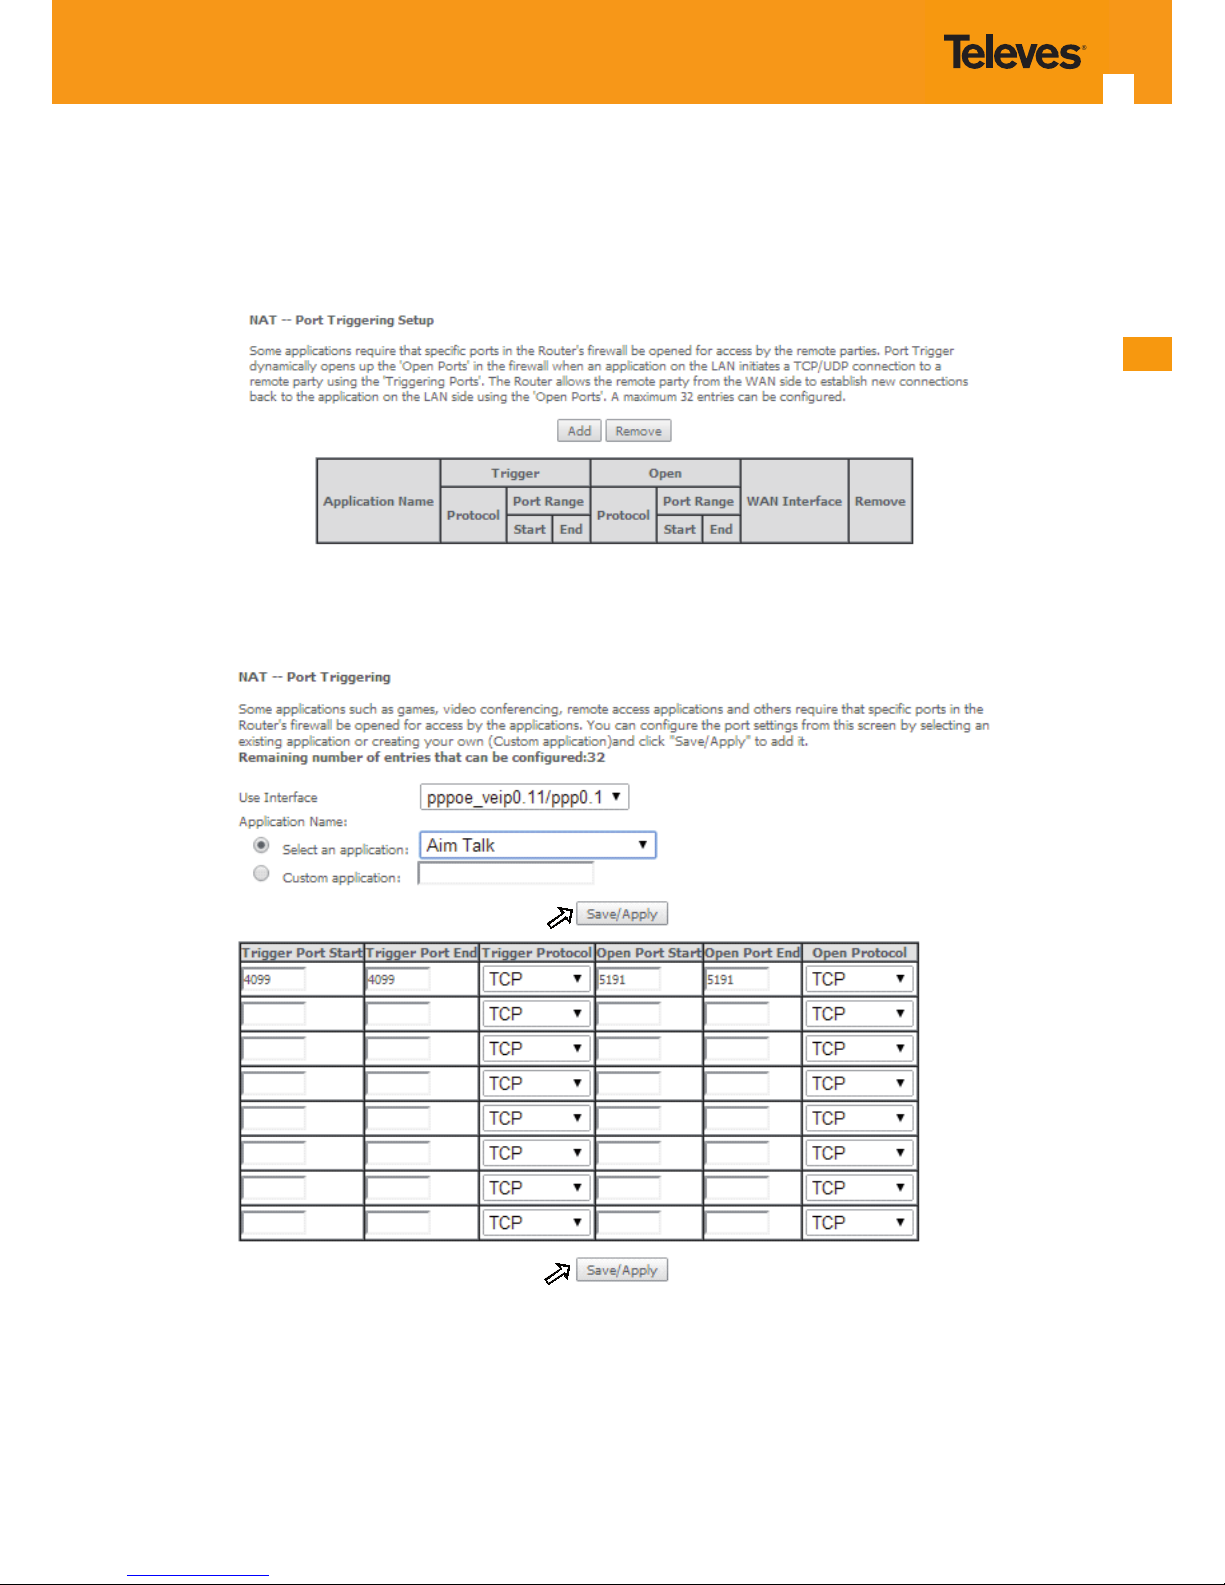
EN
87
To apply and save this conguration use the Apply/Save button, bellow Figure 5-85-1.
The port triggering table will be updated with the chosen application predened port Triggering conguration, Figure 5-84.
To nalize the conguration use the Apply/Save button below the table, Figure 85-2. The next displayed window is the initial window, showing the
current NAT - Port Triggering conguration, Figure 5-86.
Figure 5-84: Advanced Setup/NAT-Port Triggering Setup window
1
2
Figure 5-85: Advanced Setup/NAT-Port Triggering Setup window -Add port triggering for specied application
Page 88
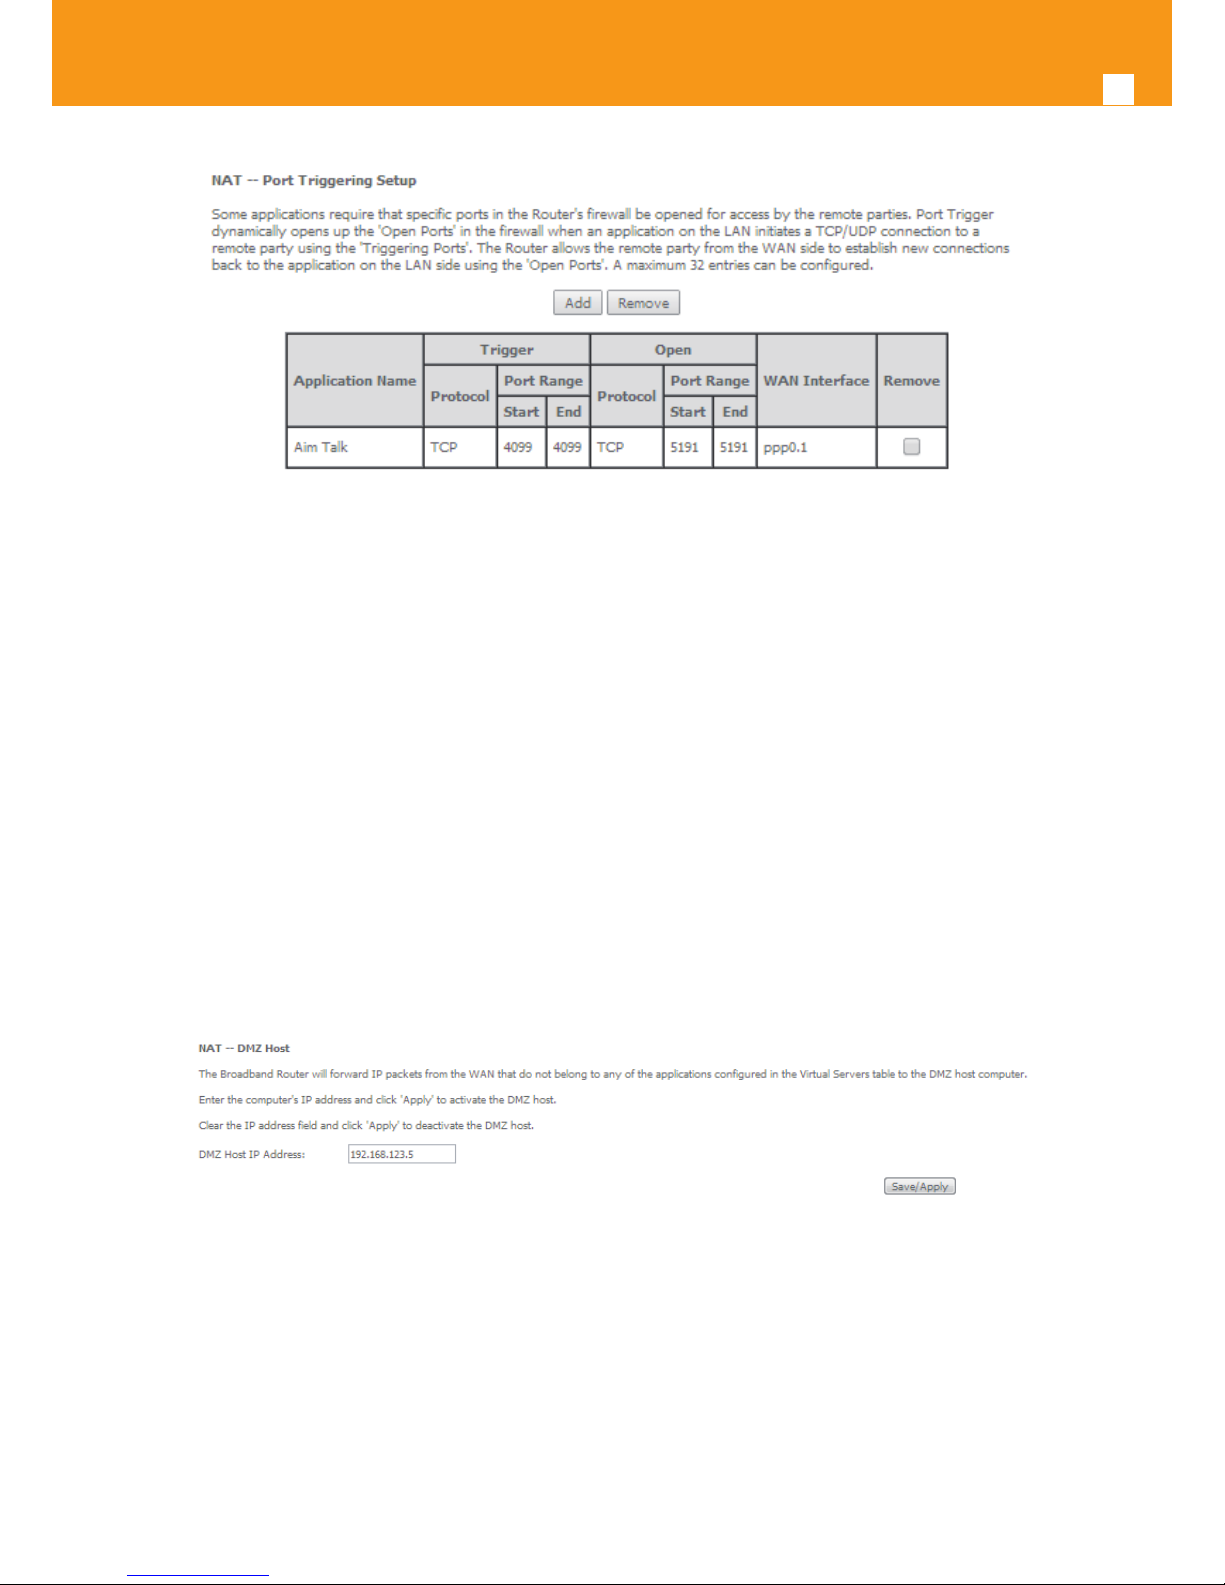
88
GPON ONT
Figure 5-86: Advanced Setup/NAT-Port Triggering Setup window -Current conguration
5.6.4.3 DMZ Host
Selection of Advanced Setup submenu NAT, item DMZ Host, a NAT-DMZ Host Setup window is displayed in the main window Figure 5-87, allowing
the DMZ Host conguration by Providing the DMZ Host IP address. A short on line help text is provided in the setup window.
A DMZ Host is a host exposed to the internet. All incoming IP packets from the WAN network side, if not belong to any Service or application
congured on the NAT- Virtual server or Port Triggering (for the apllcation) are forwarded to the DMZ Host. DMZ Host must have a static IP address
assigned to it.
To nalize the conguration use the Save/ Apply button.
Figure 5-87: Advanced Setup/NAT-DMZ Host Setup window
Page 89
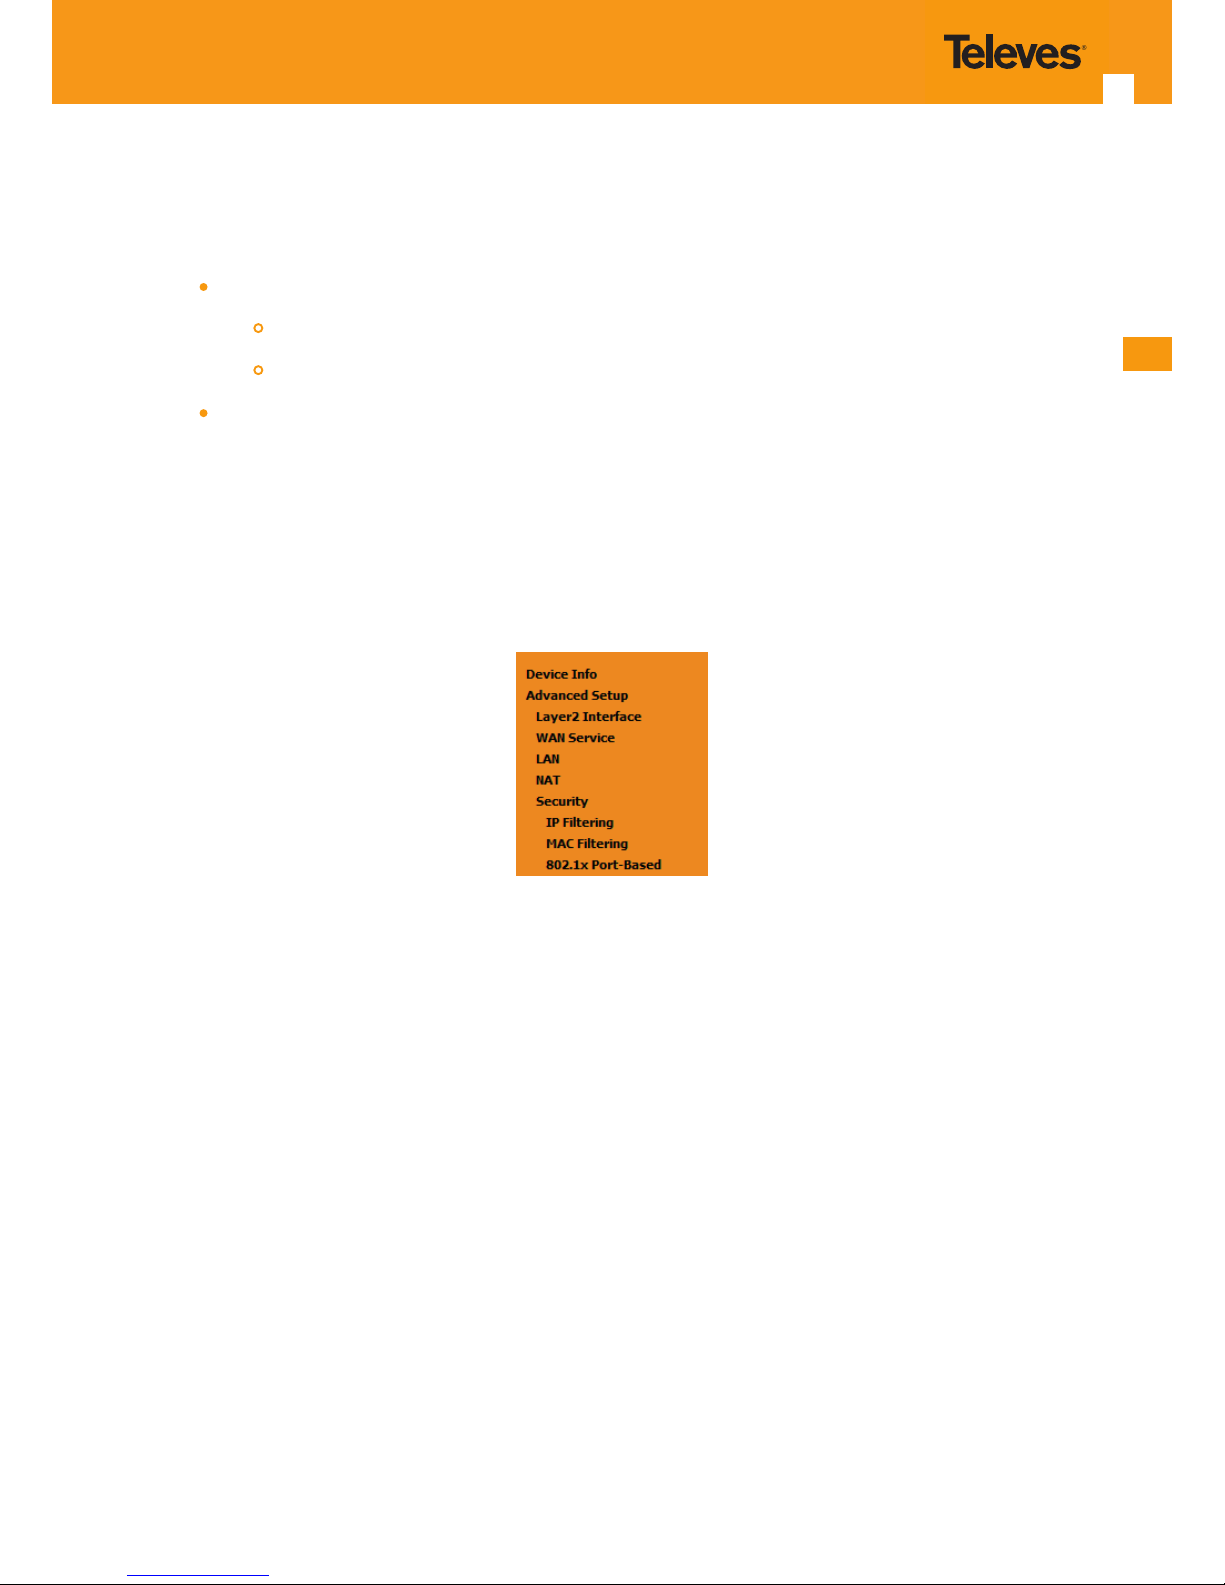
EN
89
5.6.5 Security
Selection of Advanced Setup submenu item Security will display a Security submenu with two items, Item IP Filtering is a submenu composed of
two items, Outgoing and Incoming, Figure 5-88:
IP Filtering,
Outgoing
Incoming
MAC Filtering
In the main window an Outgoing IP Filtering Setup window is displayed, Figure 5-89.
This window allows the creation and conguration a lter rule to identify outgoing IP trac.
Figure 5-88: Advanced Setup Security Sub-menu5.6.5.1 IP Filtering
Selection of Advanced Setup submenu Security, submenu IP Filtering, will display in the main window, an Outgoing IP ltering Setup window,
Figure 5-89, showing the current Outgoing IP Filtering conguration. A short on line help text is provided in the conguration window.
5.6.5.1.1 Outgoing
Selection of Advanced Setup submenu Security, submenu IP Filtering, item Outgoing, an Outgoing IP ltering Setup window is displayed , Figure
5-89, showing the current Outgoing IP Filtering conguration. A short on line help text is provided in the conguration window.
To insert and congure a new Outgoing IP Filter entry use the Add Button, Figure 5-89; a new window is displayed, Figure 108. A short on line help
text is provided in the conguration window.
This window allows the conguration of Outgoing IP Filter. Figure 5-90 provides an outgoing lter conguration example
In order to congure the Outgoing IP Filter, Figure 5-90:
STEP 1. Enter the Filter name;
STEP 2. Select the IP version to use from the IP version selection combo box;
STEP 3. Select the Protocol to use from the Protocol Selection combo box;
STEP 4. Enter the Source IP address;
Page 90
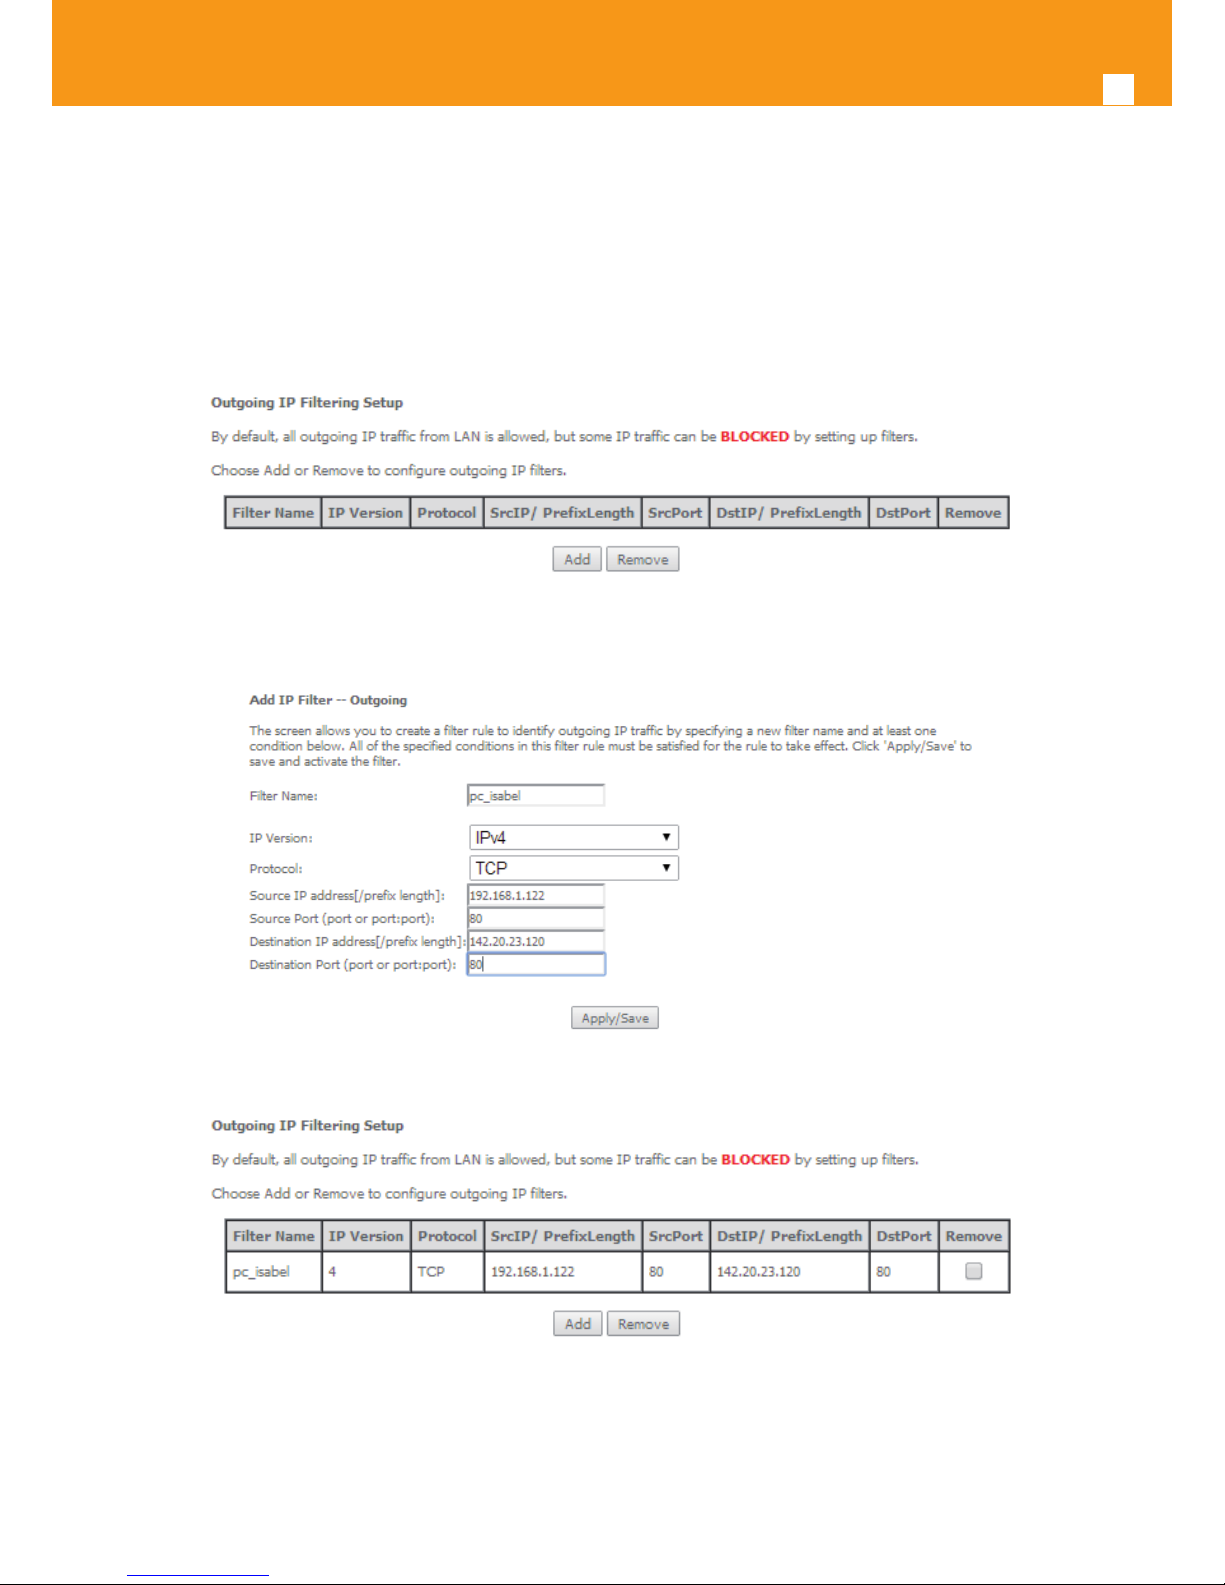
90
GPON ONT
STEP 5. Enter the Source Port;
STEP 6. Enter the Destination IP address;
STEP 7. Enter the Destination Port;
To nalize the conguration use the Apply/Save button. The next displayed window is the initial window, showing the current Outgoing IP Filtering conguration, Figure 5-91.
Figure 5-89: Advanced Setup, Security - Outgoing IP ltering Setup window
Figure 5-90:Advanced Setup, Security - Outgoing IP ltering Setup –Add Filter window
Figure 5-91: Advanced Setup, Security - Outgoing IP ltering Setup window –Current Conguration
Page 91
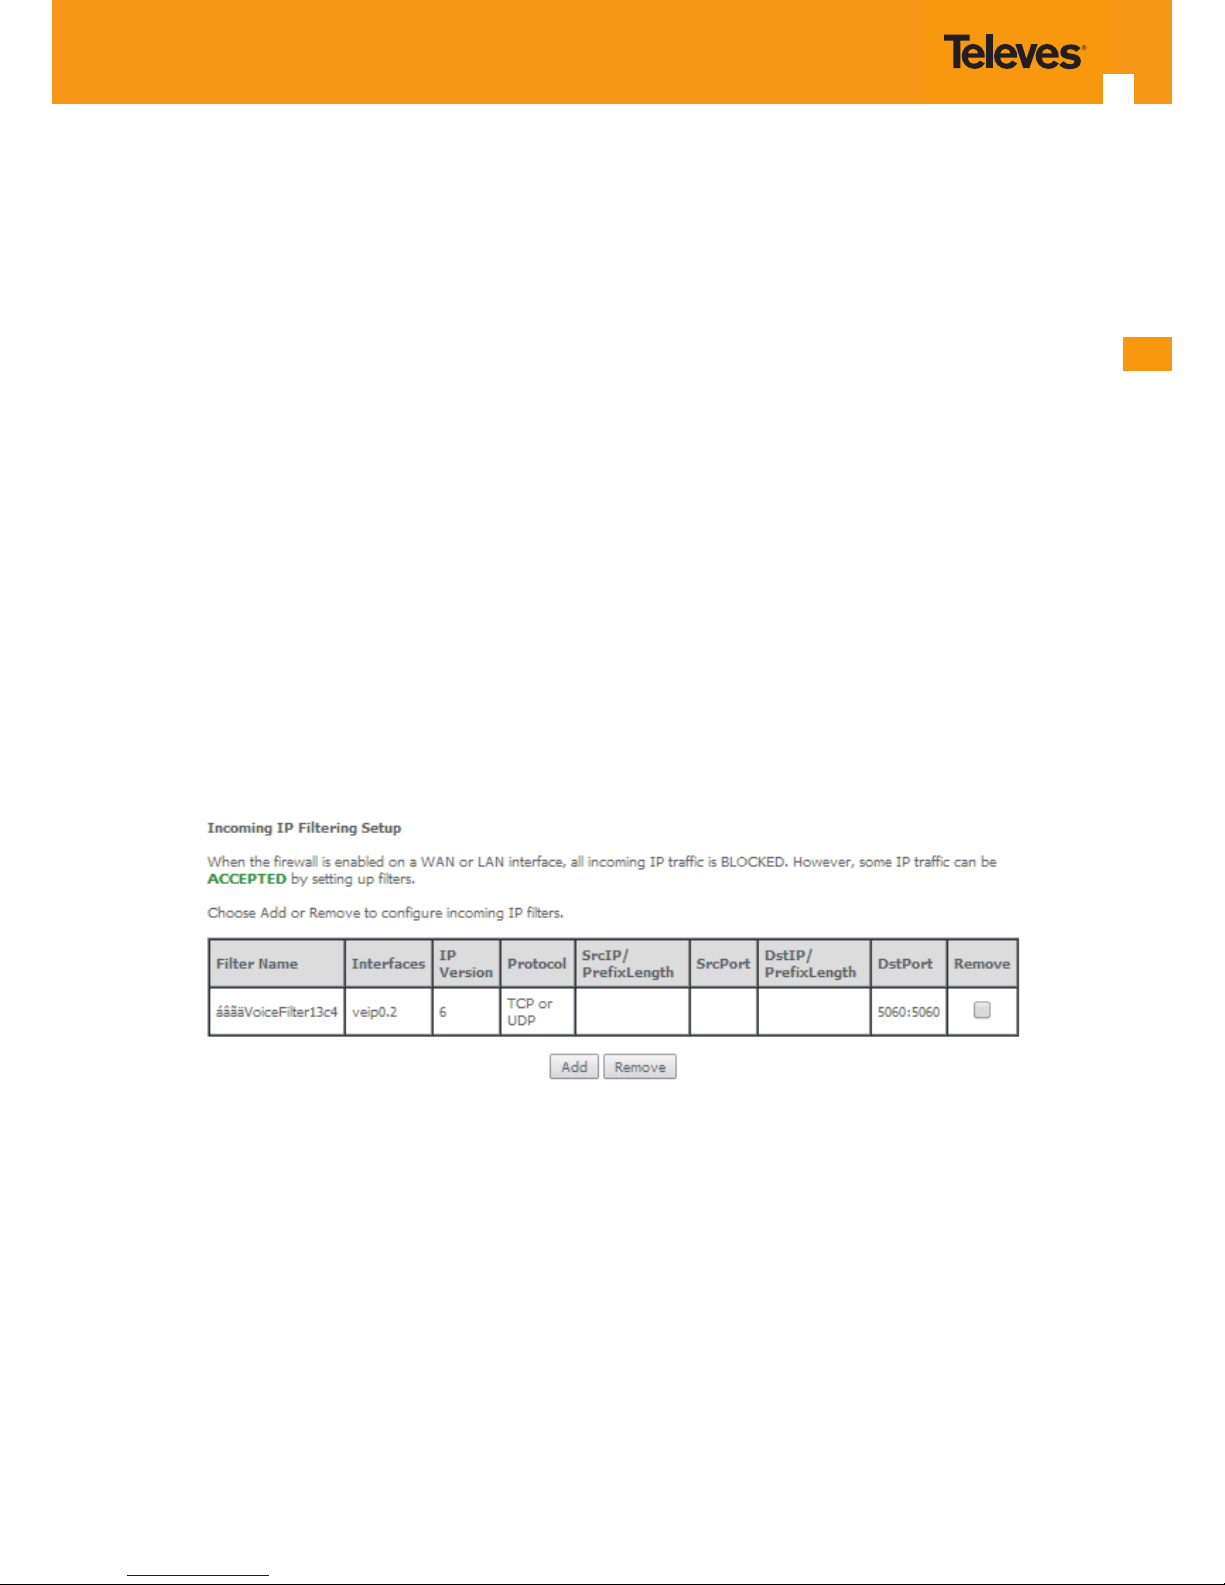
EN
91
5.6.5.1.2 Incoming
Selection of Advanced Setup submenu Security, submenu IP Filtering, item Incoming, will display an Incoming IP ltering Setup window, Figure
5-92, showing the current Incoming IP Filtering conguration. A short on line help text is provided in the conguration window.
To insert and congure a new Incoming IP Filter entry use the Add Button, Figure 110; a new window is displayed, Figure 5-93. A short on line help
text is provided in the conguration window.
This window allows the conguration of Incoming IP Filter. In order to congure the Incoming IP Filter, Figure 5-93:
STEP 1. Enter the Filter name;
STEP 2. Select the IP version to use from the IP version selection combo box, Figure 5-94;
STEP 3. Select the Protocol to use from the Protocol Selection combo box;
STEP 4. Enter the Source IP address;
STEP 5. Enter the Source Port;
STEP 6. Enter the Destination IP address;
STEP 7. Enter the Destination Port;
STEP 8. Select the WAN and/or LAN interfaces to apply this rule
Figure 5-95 provides an incoming lter conguration example
To nalize the conguration use the Apply/Save button. The next displayed window is the initial window, showing the current Incoming IP Filtering conguration, Figure 5-96.
Figure 5-92: Advanced Setup, Security - Incoming IP ltering Setup window- Current Conguration
Page 92
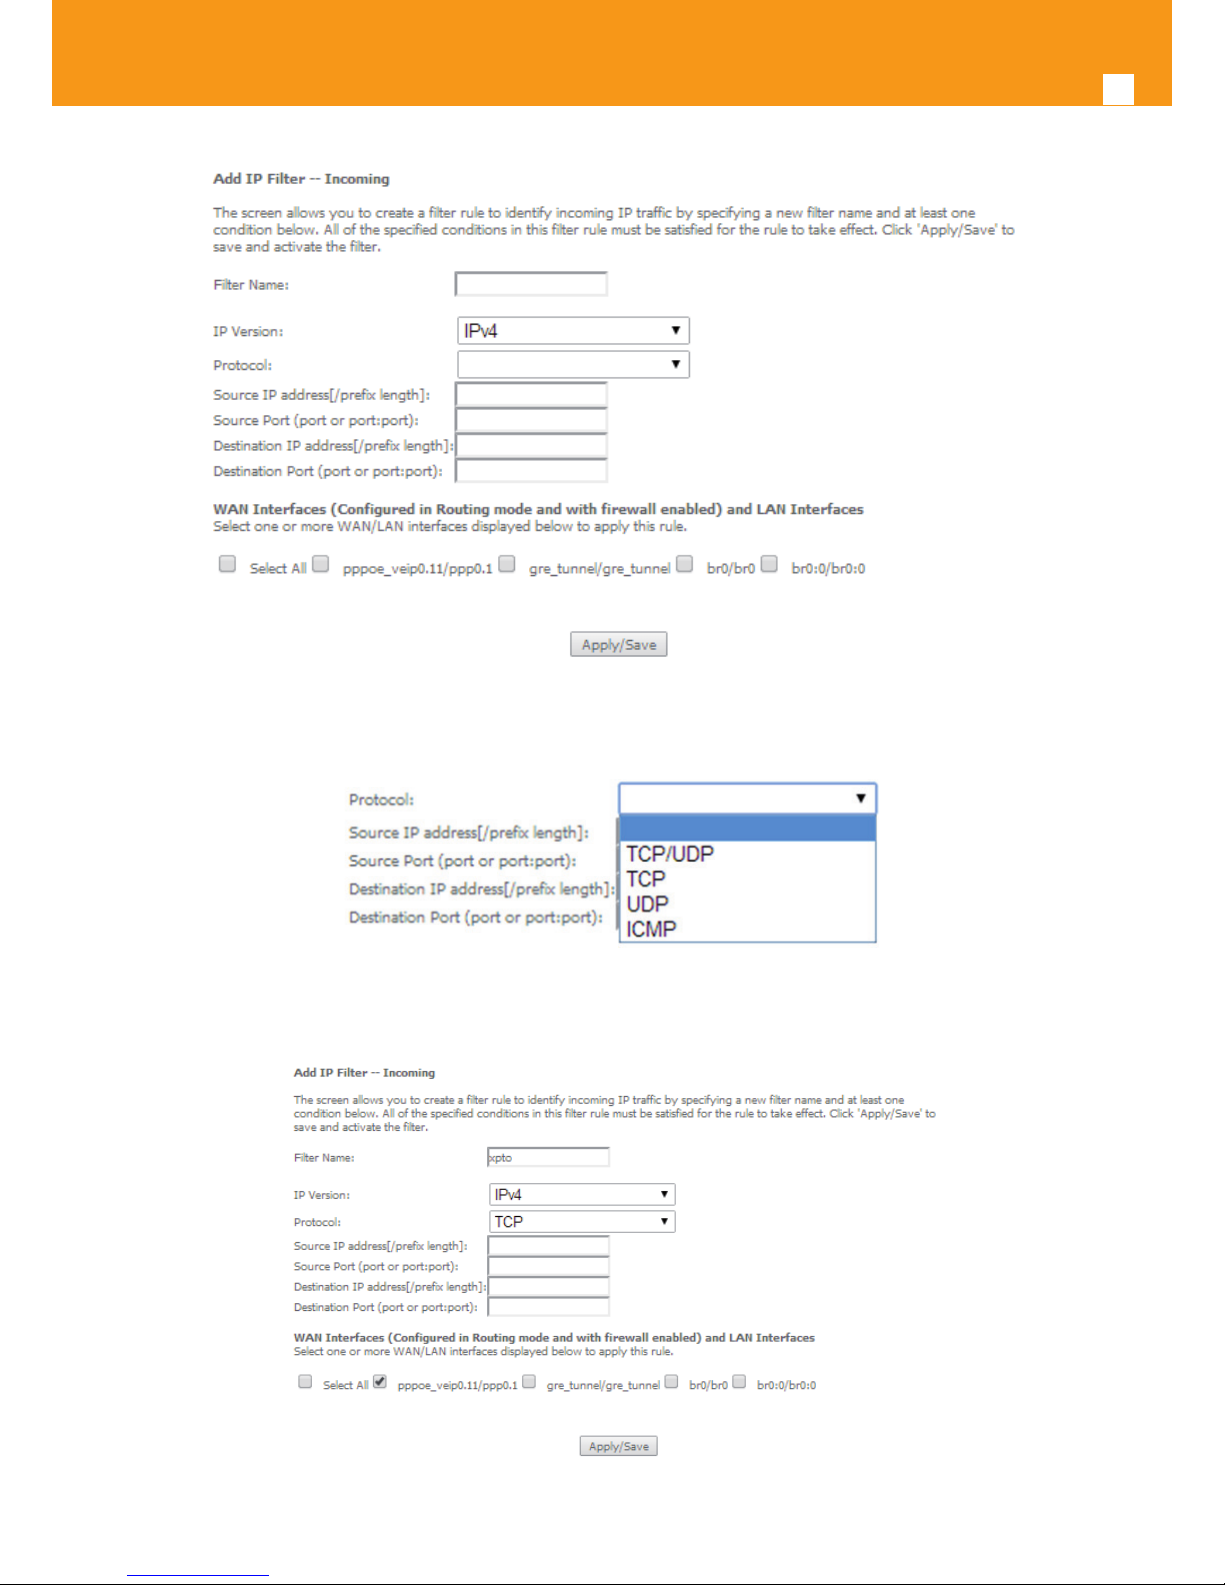
92
GPON ONT
Figure 5-93: Advanced Setup, Security - Incoming IP ltering Setup – Add Filter window
Figure 5-94: Advanced Setup, Security - Incoming IP ltering Setup- Add Filter window – Protocol selection combo box
Figure 5-95: Advanced Setup, Security - Incoming IP ltering Setup- Add Filter window - Conguration exemple
Page 93
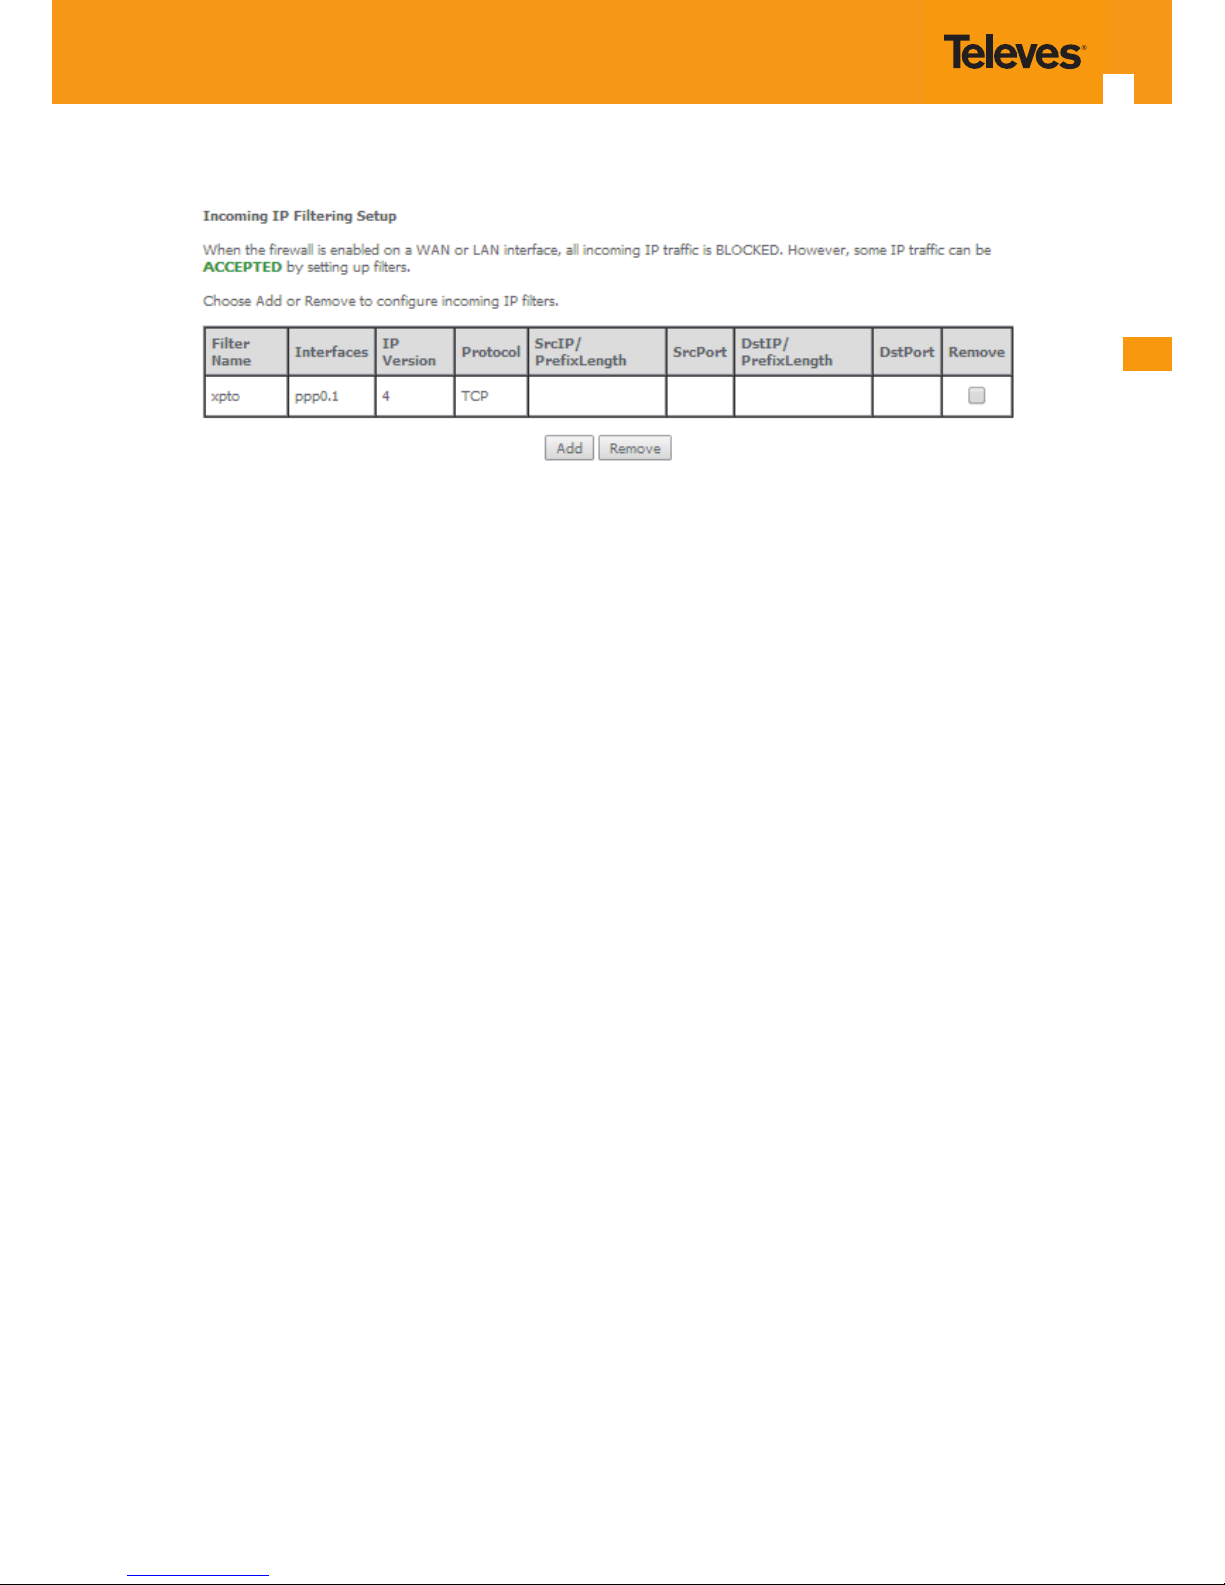
EN
93
Figure 5-96: Advanced Setup, Security - Incoming IP ltering Setup window – Current Conguration
5.6.5.2 MAC Filtering
Selection of Advanced Setup submenu Security, item MAC Filtering displays a MAC ltering Setup window, Figure 5-97, showing the current MAC
Filtering conguration: Policy and rules.
A short on line help text is provided in the conguration window.
This window allows changing the policy of rules applied: Forwarded/Blocked
If current conguration of policy is forward, all MAC layer frames are forwarded except those matching with any of the specied rules in the MAC
ltering rules table.
If current conguration of policy is blocked, all MAC layer frames are blocked except those matching with any of the specied rules in the MAC
ltering rules table.
The policy can be changed by selecting the change and afterwards use the Change policy button. The policy table will change the value to the
opposite value (from forward to blocked and vice-versa), Figure 5-98.
Changing from one policy to another of an interface will cause all dened rules for that interface to be removed automatically; therefore rules for
the new policy have to be created.
To insert and congure a new MAC ltering rule entry use the Add Button, Figure 115; a new window is displayed, Figure 5-99.
This window allows the conguration of MAC Filtering rule. A short on line help text is provided in the conguration window. Figure 5-99 provides
an outgoing lter conguration example
In order to congure the MAC Filtering rule, Figure 5-99:
STEP 1. Select the Protocol to use from the Protocol Selection combo box;
STEP 2. Type in the destination MAC address;
STEP 3. Type in the Source MAC address;
STEP 4. Select the frame direction from the selection combo box;
STEP 5. Select the WAN interfaces from the selection combo box;
To nalize the conguration use the Save/Apply button. The next displayed window is the initial window, showing the current MAC Filtering conguration, Figure 5-100.
Page 94
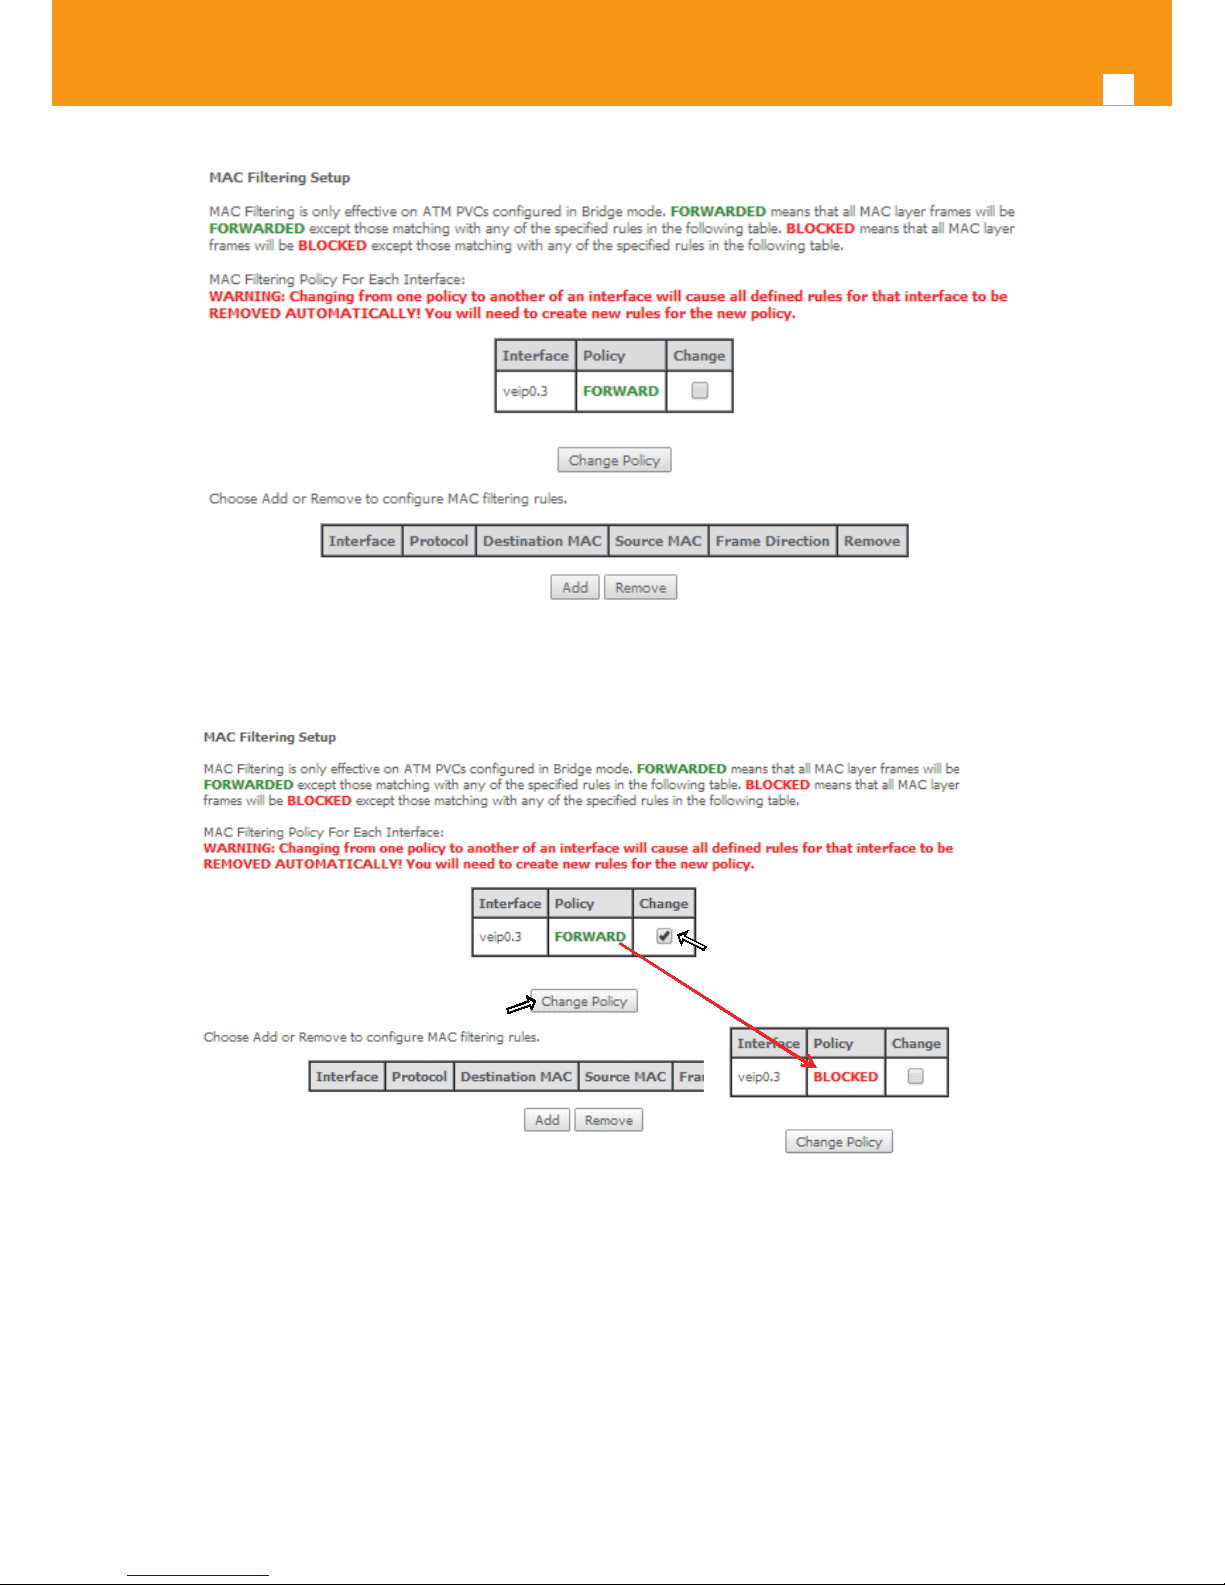
94
GPON ONT
Figure 5-97: Advanced Setup, Security – MAC ltering Setup window
1
2
Figure 5-98: Advanced Setup, Security – MAC ltering Setup window –Change policy
Page 95
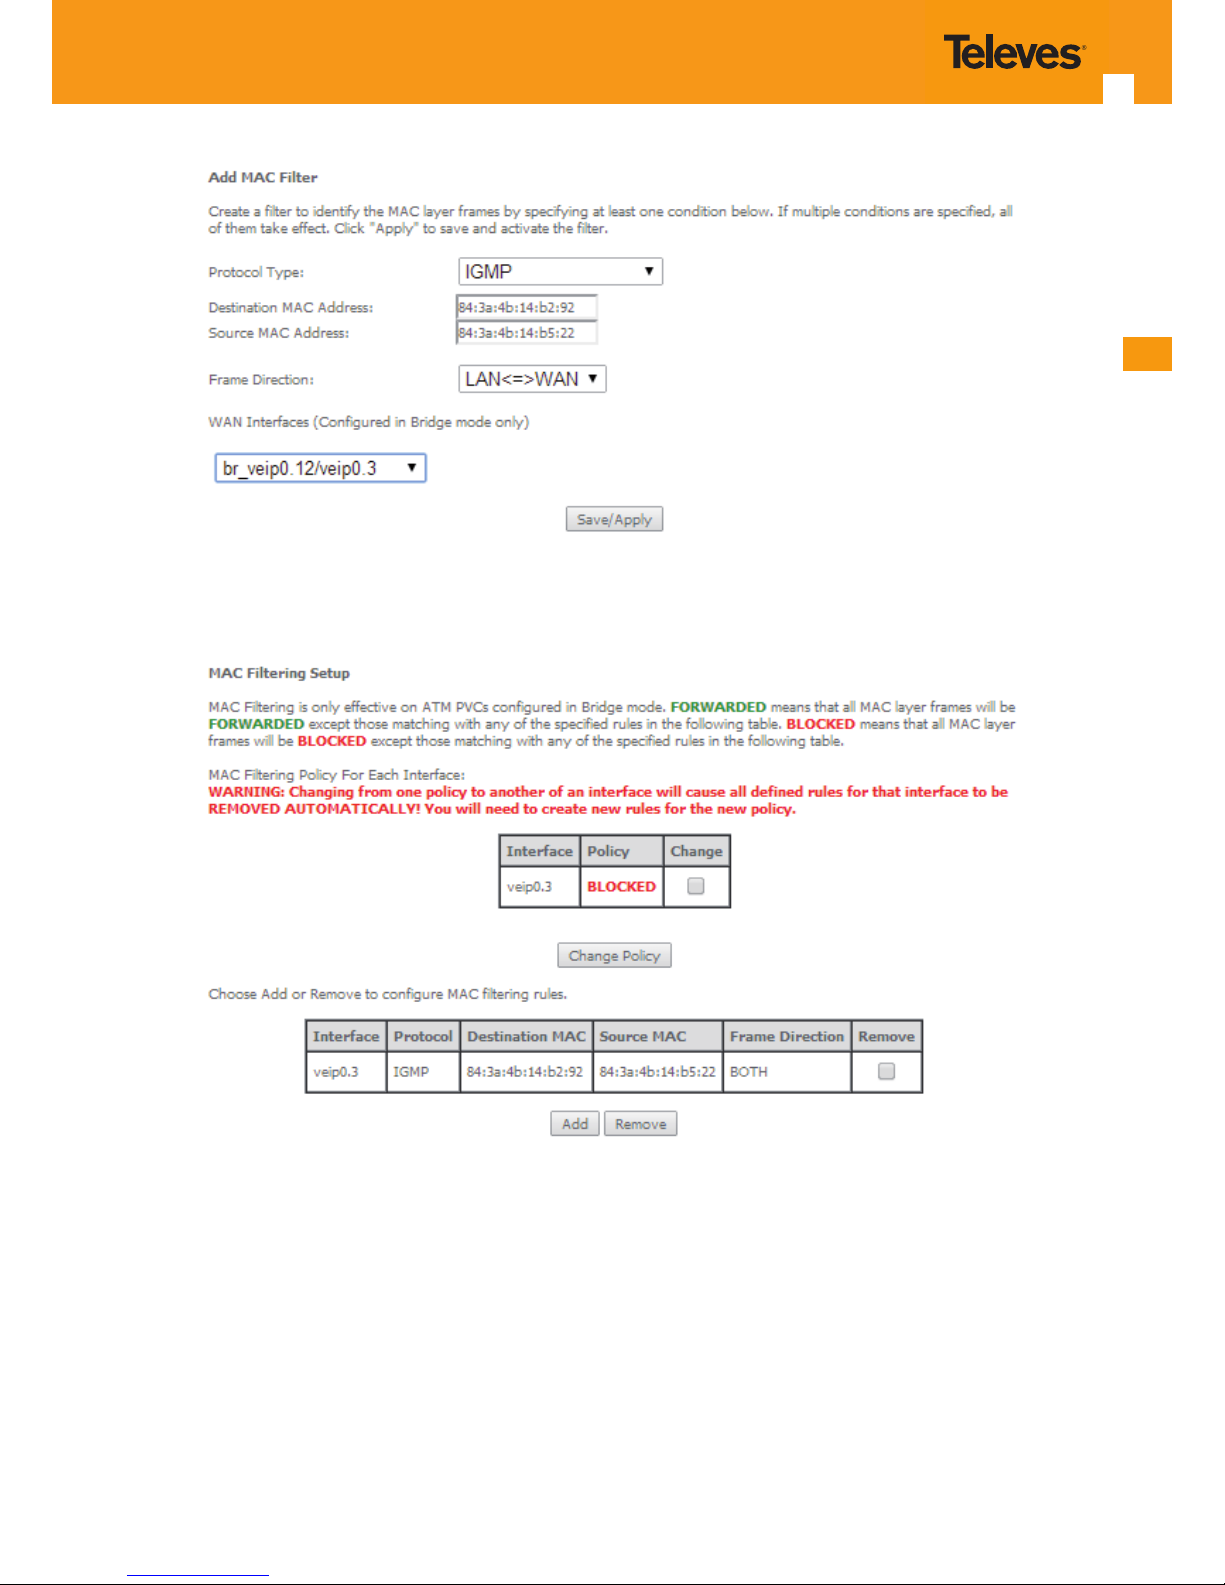
EN
95
Figure 5-99: Advanced Setup, Security – MAC ltering – Add MAC Filter window
Figure 5-100: Advanced Setup, Security – MAC ltering Setup window –Current Conguration
Page 96
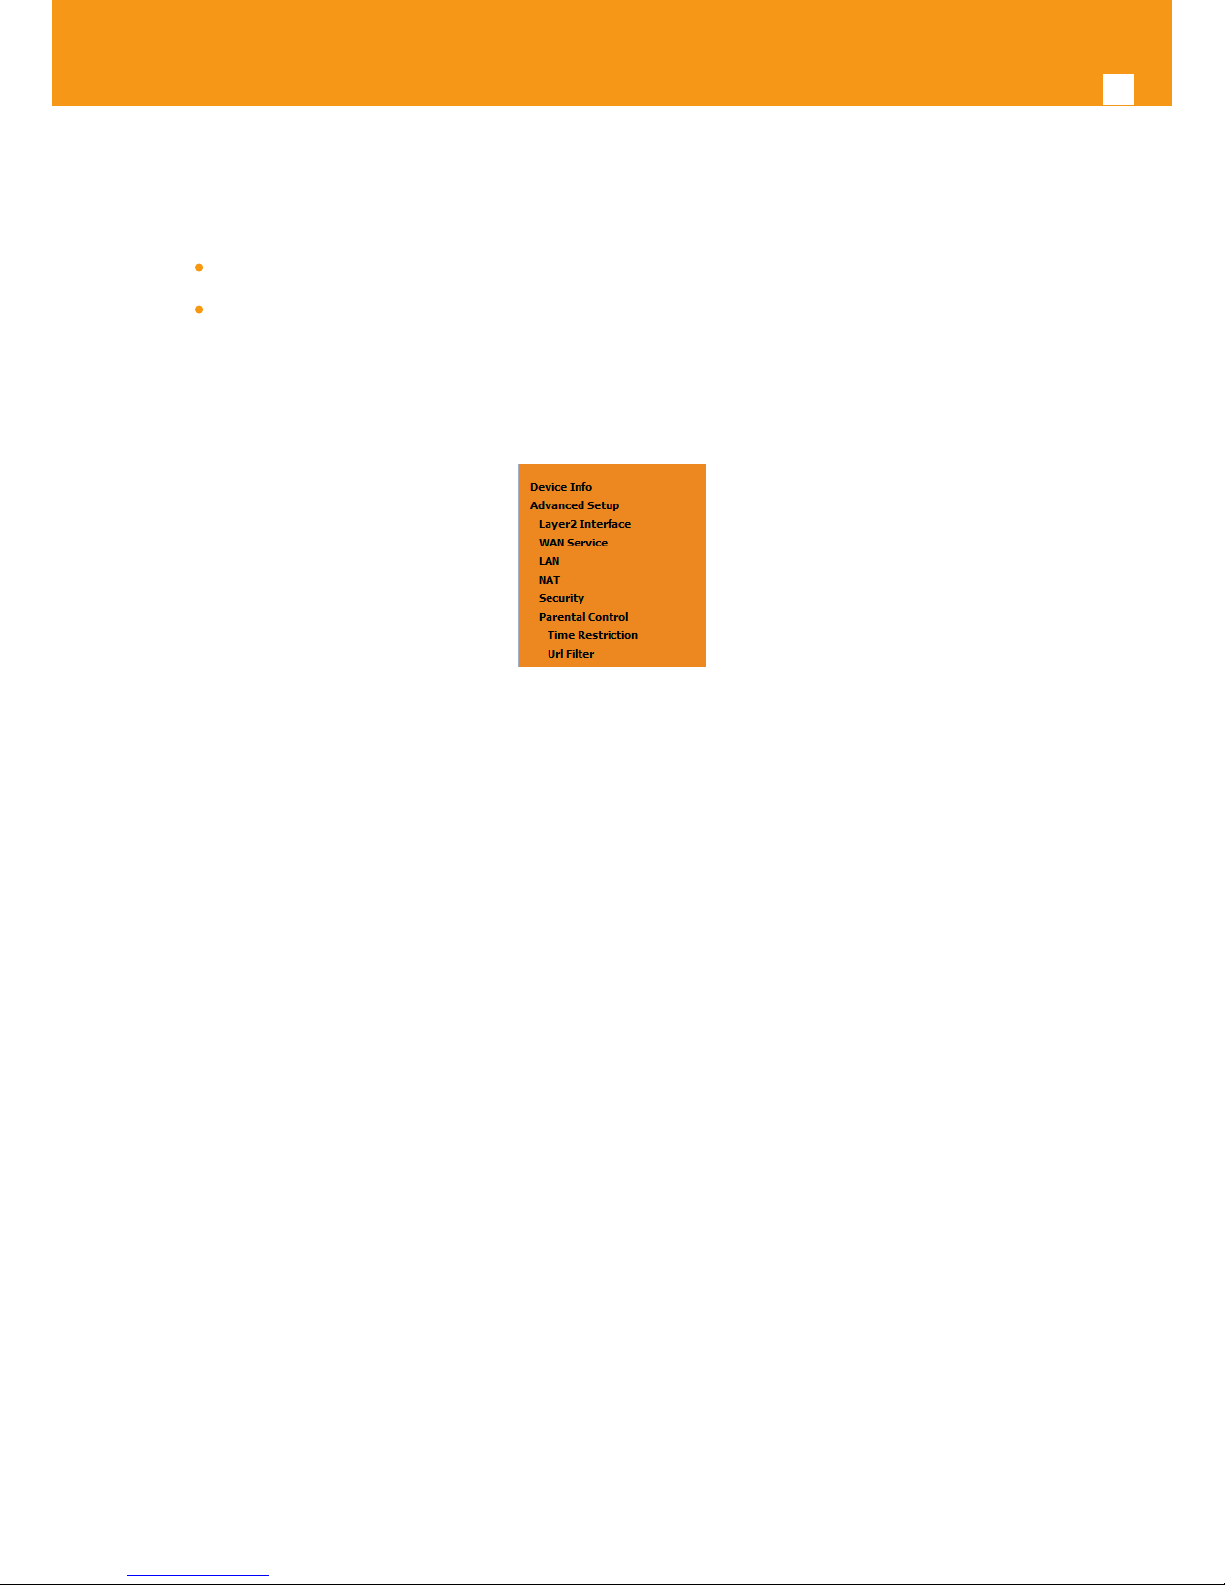
96
GPON ONT
5.6.6 Parental Control
Selection of Advanced Setup submenu item Parental Control will display a Parental Control submenu with two items, Figure 5-101:
Time Restriction,
Url Filter
In the main window an Access time Restriction Conguration window is displayed, Figure 5-102.
This window allows the creation and conguration Access Time Restriction Rules.
Figure 5-101: Advanced Setup Parental Control Sub-menu
5.6.6.1 Time Restriction
Selection of Advanced Setup submenu Parental Control, item Time Restriction will display an Access Time Restriction conguration window showing the current Access Time Restriction conguration table, Figure 5-102.
A short on line help text is provided in the conguration window.
To insert and congure a new Access Time Restriction rule use the Add Button, Figure 5-102; a new window is displayed, Figure 5-103. A short on
line help text is provided in the conguration window. Figure 5-103. Provides a conguration example for an Access Time Restriction rule.
In order to setup a new Access Time Restriction rule, Figure 5-103:
STEP 1. Enter the user name;
STEP 2. Enter the Browser’s MAC address;
STEP 3. Select the week days to apply the restriction;
STEP 4. Enter the Start Blocking time;
STEP 5. Enter the End Blocking time;
To nalize the conguration use the Apply/Save button. The next displayed window is the initial window, showing the current Access Time Restriction conguration, Figure 5-104.
Page 97
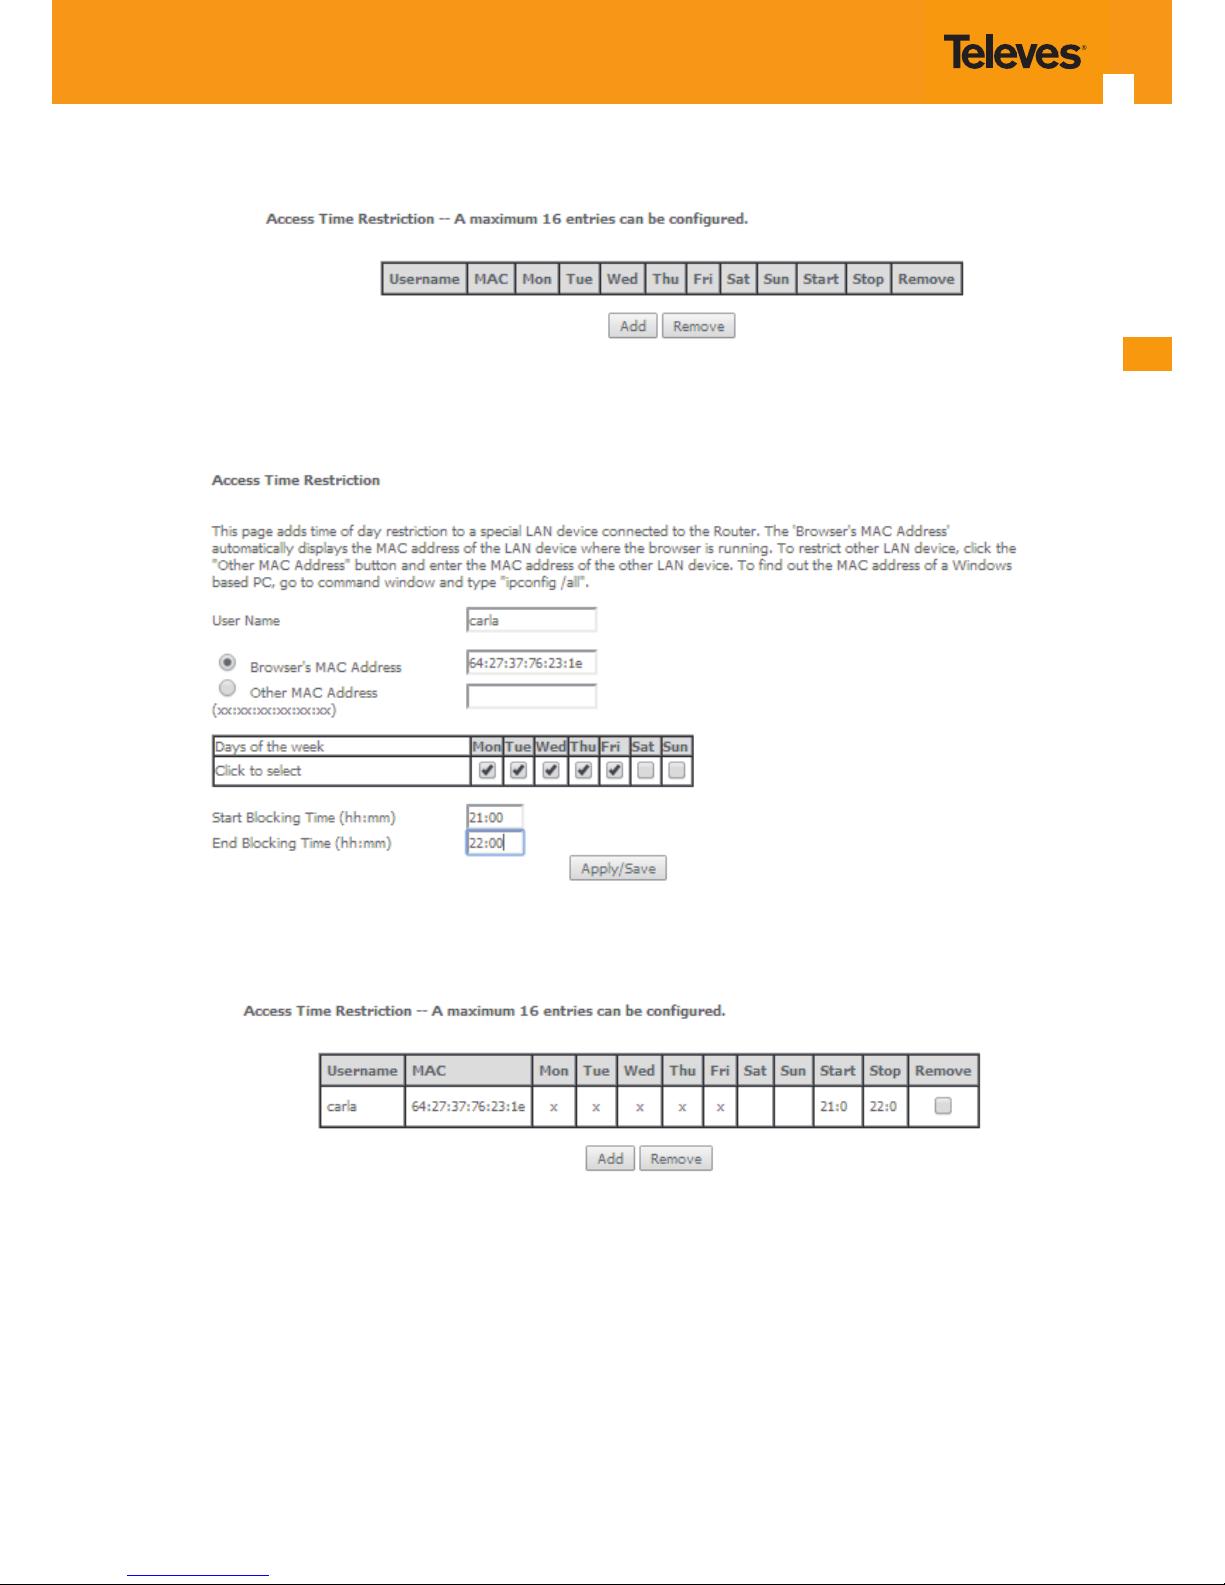
EN
97
Figure 5-102: Advanced Setup, Parental Control – Time Restriction Conguration window
Figure 5-103: Advanced Setup, Parental Control, Time Restriction -Add Time Restriction rule window
Figure 5-104: Advanced Setup, Parental Control – Time Restriction Conguration window - Current conguration
Page 98
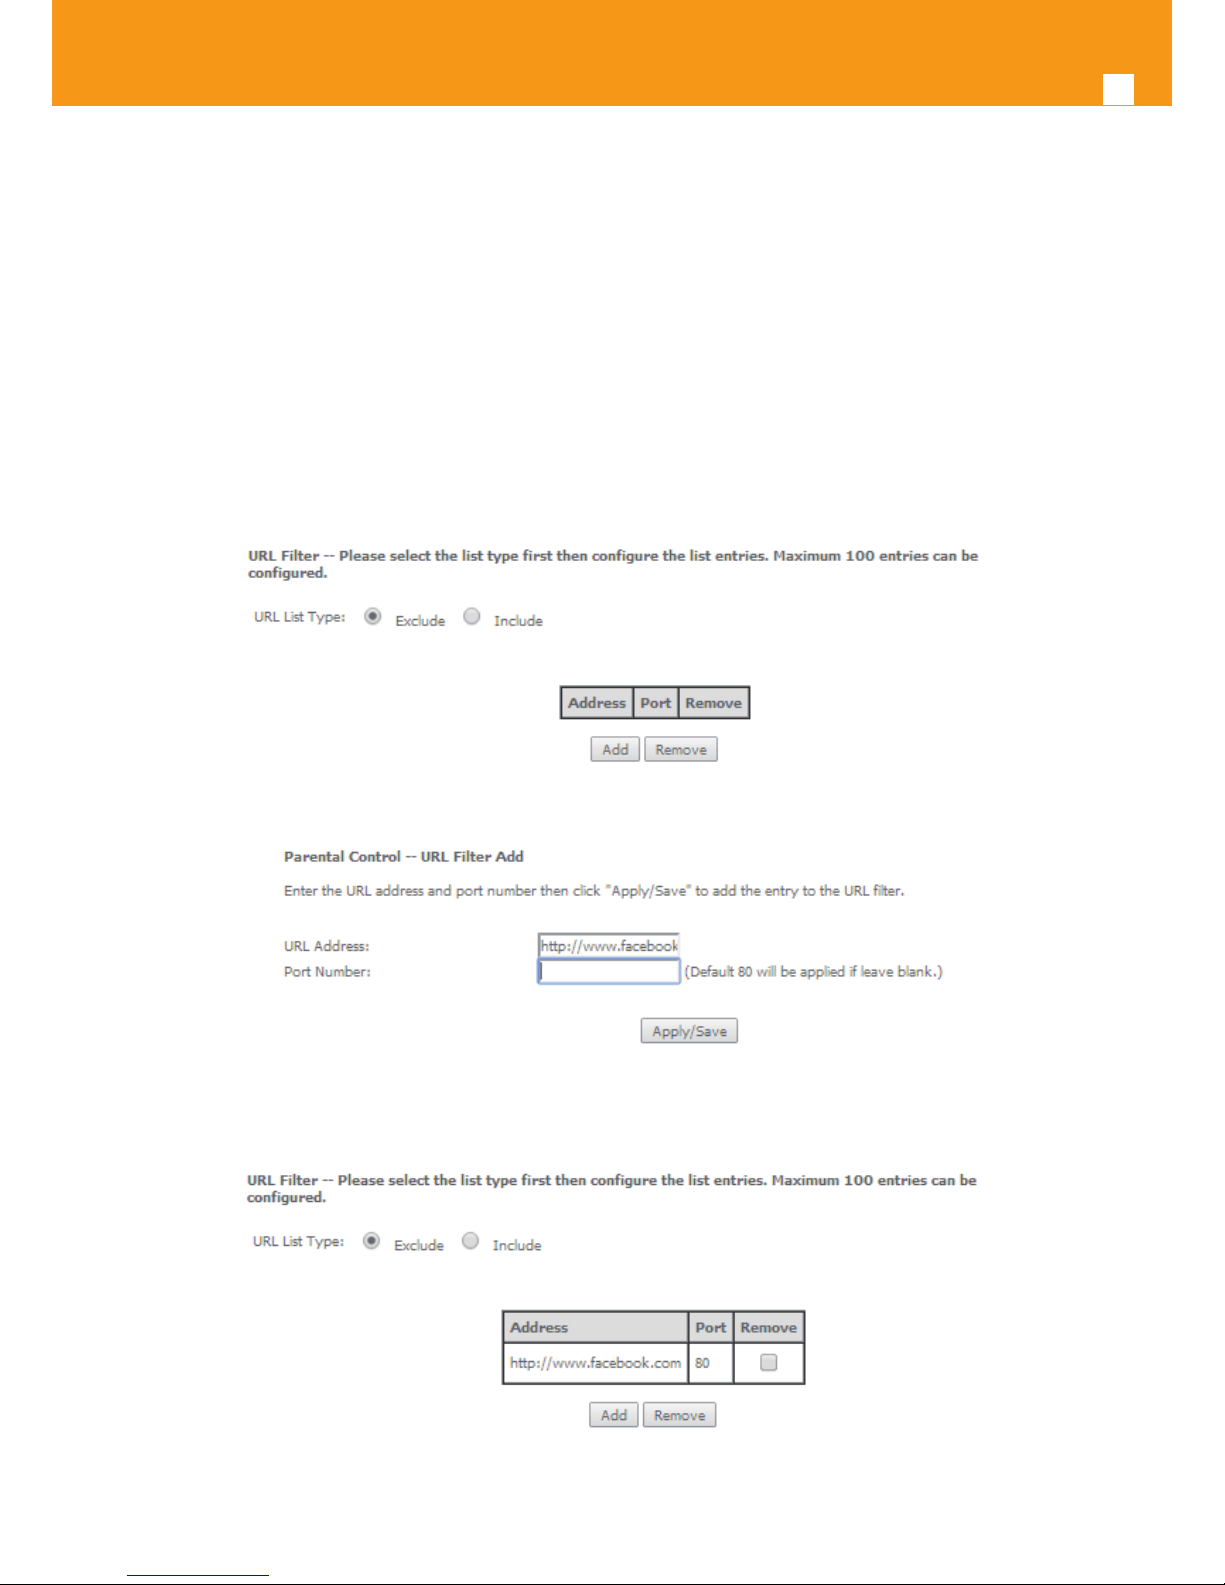
98
GPON ONT
5.6.6.2 URL Filter
Selection of Advanced Setup submenu Parental Control, item Url Filter will display an URL Filter conguration window showing the current URL
Filter conguration table, Figure 5-105. This window allows the creation and conguration of an URL Filter list.
A short on line help text is provided in the conguration window Figure 5-105.
To create a URL lter list the URL list Type to create must be dened as Exclude or Include, Figure 5-105.
To create a new entry in the URL lter list, use the Add button, Figure 123; an URL Filter Add window will be displayed, Figure 5-106.
In this window enter the URL address. Default port number 80 will be used if Port number entry is left blank.
To nalize the add URL entry to the URL lter list use the Apply/Save button, Figure 124. The next displayed window is the initial window, showing
the current URL Filter conguration, Figure 5-107.
Figure 5-105: Advanced Setup, Parental Control – URL Filter Conguration window
Figure 5-106: Advanced Setup, Parental Control – URL Filter – Add Filter window
Figure 5-107: Advanced Setup, Parental Control – URL Filter Conguration window- Current Conguration
Page 99
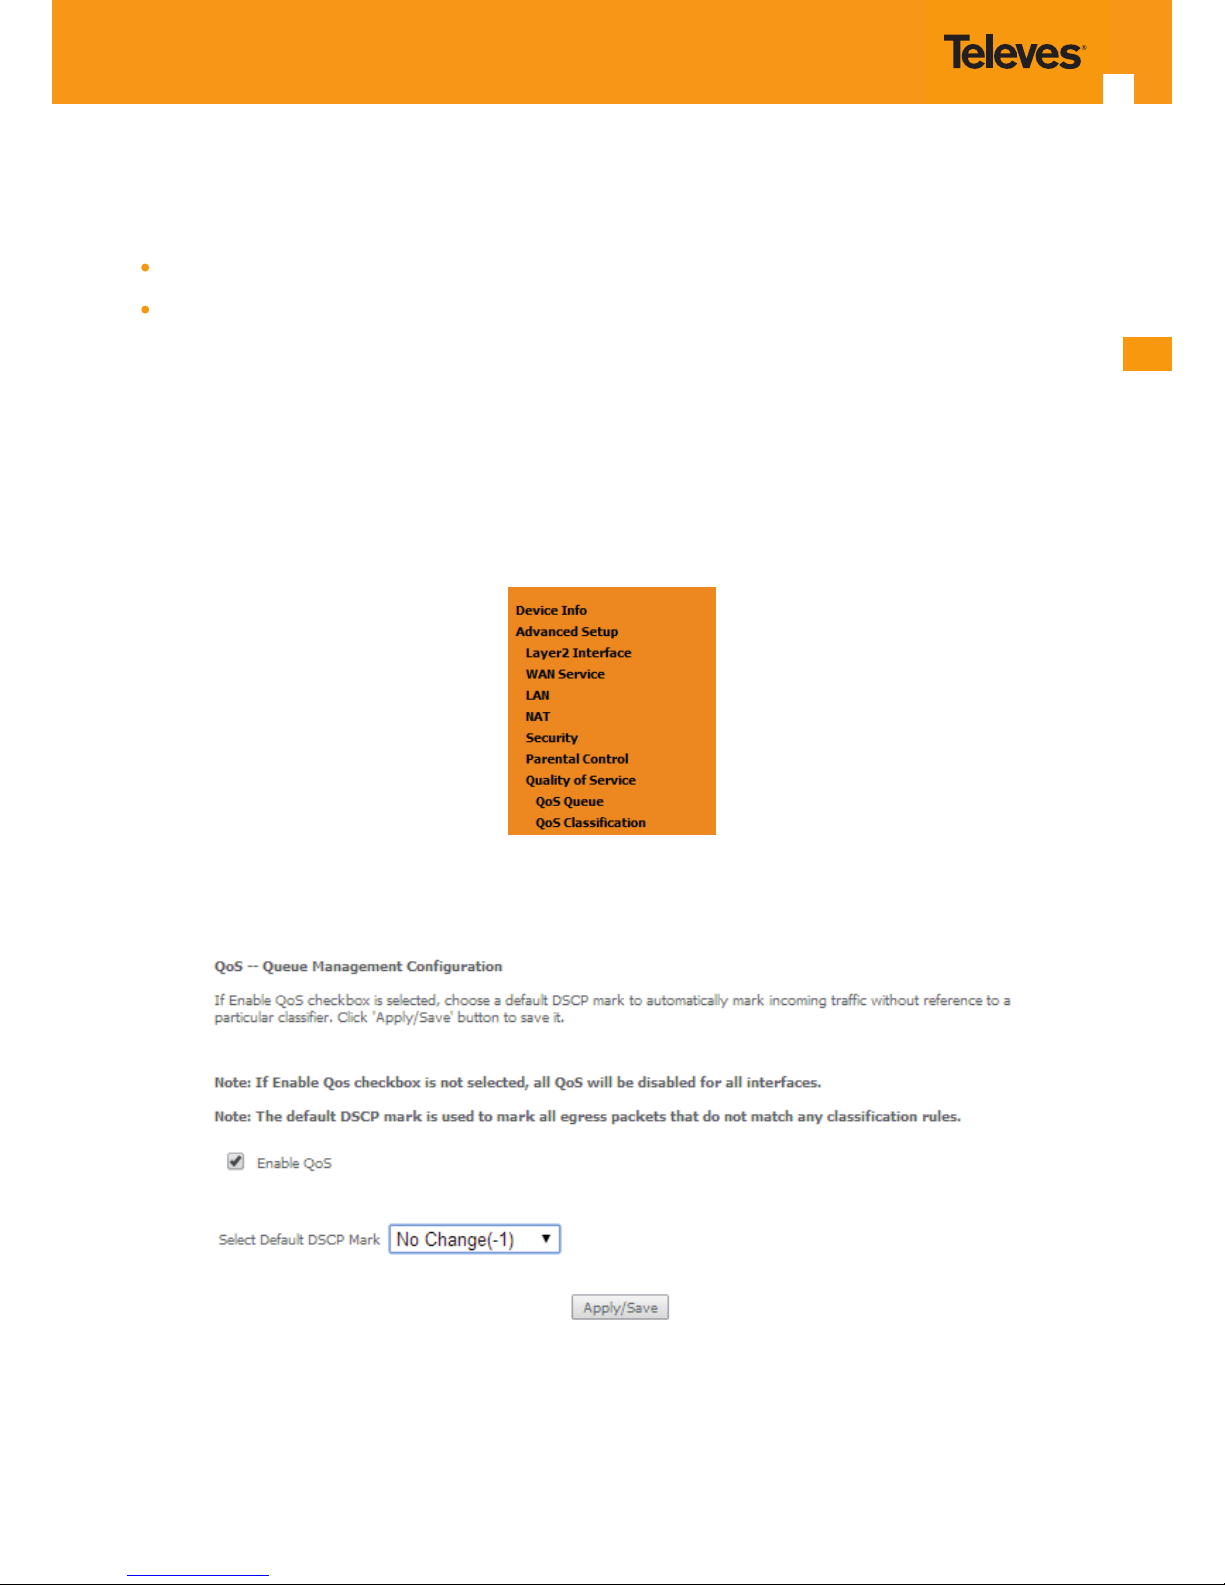
EN
99
5.6.7 Quality of Service
Selection of Advanced Setup submenu item Quality of Service will display a Quality of Service submenu with two items, Figure 5-108:
QoS Queue,
QoS Classication
This Submenu allows QoS conguration. It is assumed that the Refs. 769501-769502 has the following services already congured: IPoE with NAT
and PPPoE services.
In the main window a QoS Queue Management Conguration window will be displayed, Figure 5-109
QoS is disabled by default - it must be enabled by selecting the Enable QoS option, Figure 5-109. Default DSCP mark can be selected from a selection combo box, Figure 5-110. Use the button Apply/Save to apply this conguration and progress to the next window,
Figure 5-108: Advanced Setup Quality of Service Sub-menu
Figure 5-109: Advanced Setup Quality of Service -Queue Management Conguration
Page 100
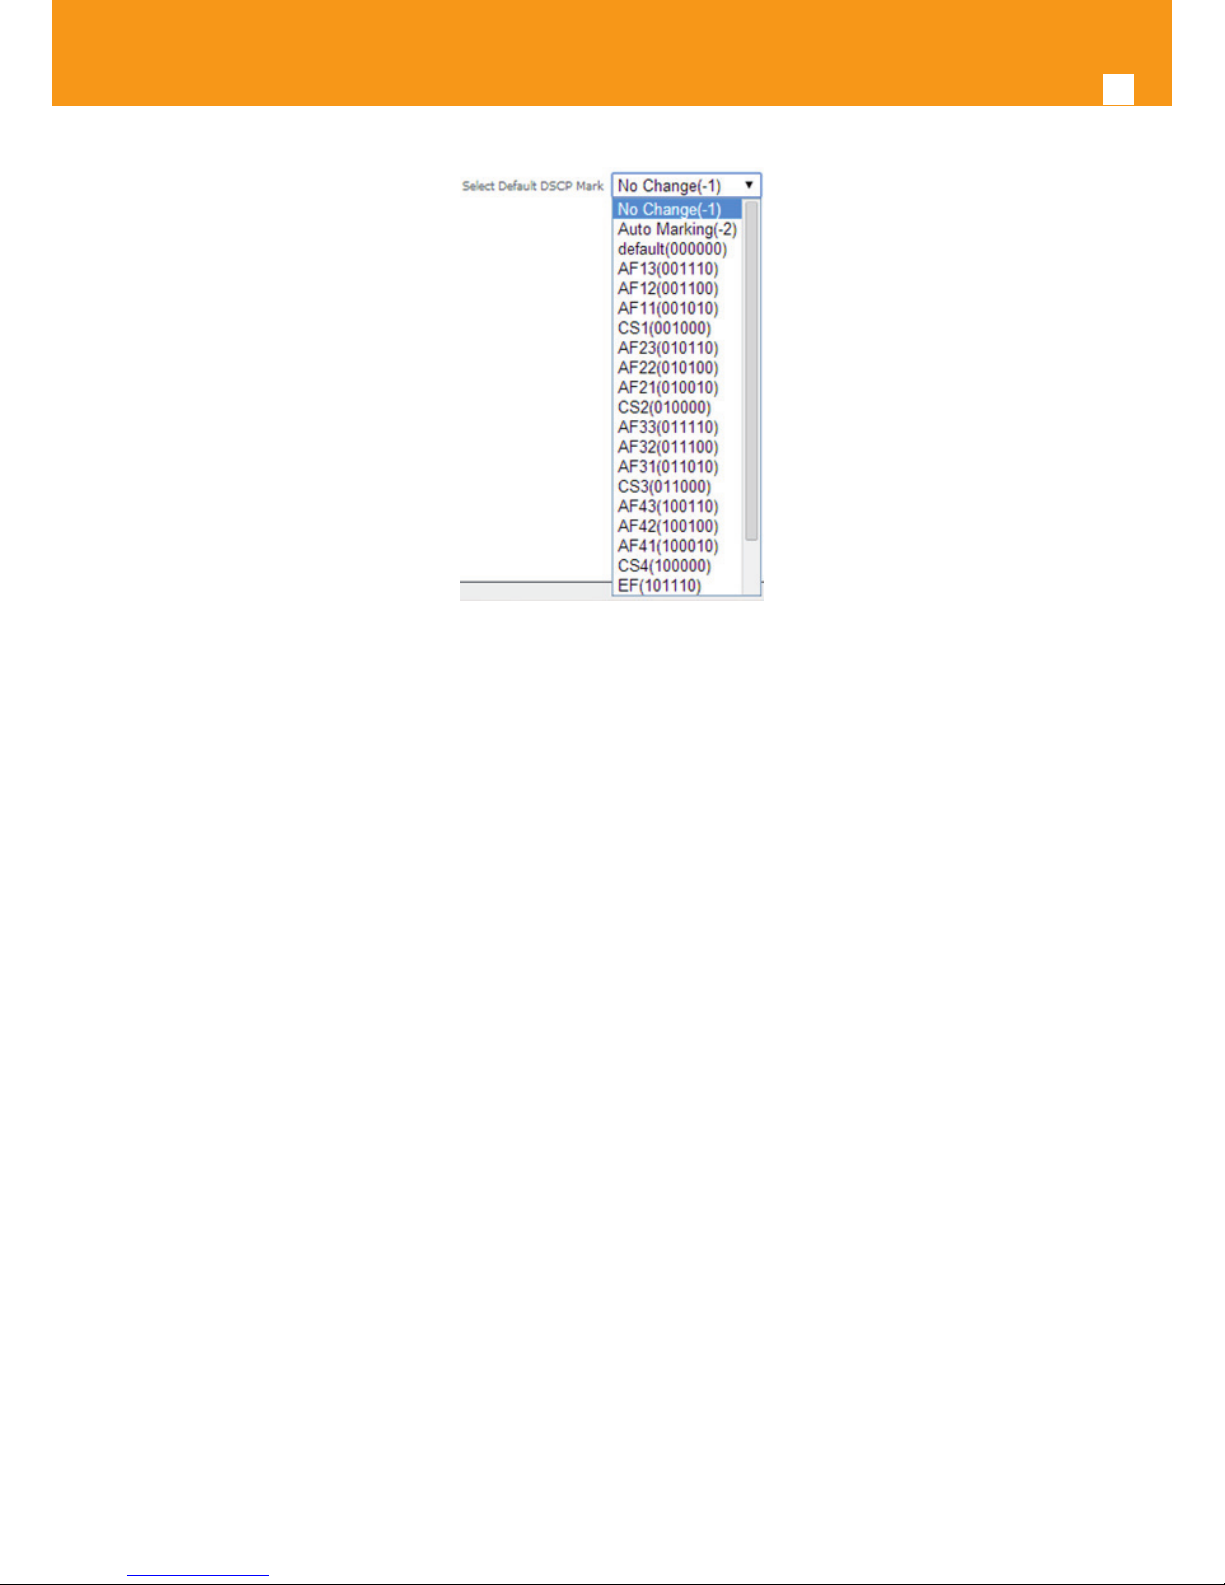
100
GPON ONT
Figure 5-110: Advanced Setup Quality of Service- Queue Management Conguration- Select Default DSCP mark combo box
5.6.7.1 QoS Queue
Selection of Advanced Setup submenu Quality of Service, item QoS Queue will display a QoS Queue Setup Conguration window, Figure 5-111.
This window displays the current QoS congured queues.
A short on line help text is provided in the conguration window.
To insert and congure a new QoS queue entry use the Add Button, Figure 5-111; a new window is displayed, Figure 5-112. A short on line help
text is provided int the conguration window. Figure 5-113 provides a conguration example.
In order to congure a new QoS queue, Figure 5-113:
STEP 1. Enter the QoS queue name;
STEP 2. Select Enable/Disable from the Enable selection combo box; a queue congured as disable can be later on enabled at the current
QoS queue conguration window, Figure 5-114 and Figure 5-118
STEP 3. Select the Interface for the QoS queue from a selection combo box;
STEP 4. Select the queue precedence from a selection combo box;
The Lower is the selected value for queue precedence the higher is the priority; along with the precedence level, the scheduler algorithm for each
precedence level is show; queues with the same precedence will bw scheduled based on the algorithm; queues with unequal precedence will be
scheduled based on SP (Strict Priority).
To nalize the conguration use the Apply/Save button. The next displayed window is the initial window, showing the current Access QoS queue
conguration, Figure 5-114.
 Loading...