

Page 1
C-300 Series Gigabit Managed Switch
CLI Reference Guide
SOFTWARE RELEASE
1.1.10.171
V
www.signamax.com
Page 2
CLI Reference Guide
SC30010
C-300 48 Port Gigabit Managed Switch
E122017-KS-R01
Page 3
How to Use This Guide
This guide includes detailed information on the switch software, including how
to operate and use the management functions of the switch. To deploy this
switch effectively and ensure trouble-free operation, you should first read the
relevant sections in this guide so that you are familiar with all of its software
features.
Who Should Read
This Guide?
How This Guide is
Organized
Related
Documentation
This guide is for network administrators who are responsible for operating and
maintaining network equipment. The guide assumes a basic working
knowledge of LANs (Local Area Networks), the Internet Protocol (IP), and
Simple Network Management Protocol (SNMP).
This guide describes the switch’s command line interface (CLI). For more
detailed information on the switch’s key features or information about the web
browser management interface refer to the Web Management Guide.
The guide includes these sections:
◆ Section I “Getting Started” — Includes information on initial configuration.
◆ Section II “Command Line Interface” — Includes all management options
available through the CLI.
◆ Section III “Appe nd ice s” — Includes information on troubleshooting switch
management access.
This guide focuses on switch software configuration through the CLI.
For information on how to manage the switch through the Web management
interface, see the following guide:
Web Management Guide
For information on how to install the switch, see the following guide:
Installation Guide
For all safety information and regulatory statements, see the following
documents:
– 3 –
Page 4
How to Use This Guide
Conventions The following conventions are used throughout this guide to show information:
Quick Start Guide
Safety and Regulatory Information
Note:
features or instructions.
Caution:
damage the system or equipment.
Emphasizes important information or calls your attention to related
Alerts you to a potential hazard that could cause loss of data, or
Revision History This section summarizes the changes in each revision of this guide.
Revision Date ChangeDescription
v1.1.10.171 12/2017 Initialrelease
– 4 –
Page 5
Contents
How to Use This Guide 3
Contents 5
Tables 29
SECTION I GETTING STARTED 34
1 Initial Switch Configuration 35
Connecting to the Switch 35
Configuration Options 35
Connecting to the Console Port 36
Logging Onto the Command Line Interface 37
Setting Passwords 37
Remote Connections 38
Configuring the Switch for Remote Management 39
Using the Network Interface 39
Setting an IP Address 39
Enabling SNMP Management Access 45
Managing System Files 47
Upgrading the Operation Code 48
Saving or Restoring Configuration Settings 48
Automatic Installation of Operation Code and Configuration Settings 50
Downloading Operation Code from a File Server 50
Specifying a DHCP Client Identifier 53
Downloading Configuration Files / Other Parameters from a DHCP Server 54
Setting the System Clock 56
Setting the Time Manually 57
Configuring SNTP 57
Configuring NTP 58
– 5 –
Page 6
Contents
SECTION II COMMAND LINE INTERFACE 59
2 Using the Command Line Interface 61
Accessing the CLI 61
Console Connection 61
Telnet Connection 62
Entering Commands 63
Keywords and Arguments 63
Minimum Abbreviation 63
Command Completion 64
Getting Help on Commands 64
Partial Keyword Lookup 66
Negating the Effect of Commands 66
Using Command History 66
Understanding Command Modes 66
Exec Commands 67
Configuration Commands 68
Command Line Processing 69
Showing Status Information 70
CLI Command Groups 71
3 General Commands 73
prompt 73
reload (Global Configuration) 74
enable 75
quit 76
show history 76
configure 77
disable 78
reload (Privileged Exec) 78
show reload 79
end 79
exit 79
4 System Management Commands 81
– 6 –
Page 7
Contents
Device Designation 81
hostname 82
System Status 82
show access-list tcam-utilization 83
show license file 84
show memory 85
show process cpu 85
show process cpu guard 86
show process cpu task 87
show running-config 88
show startup-config 90
show system 90
show tech-support 92
show users 93
show version 93
show watchdog 94
watchdog software 94
Fan Control 95
fan-speed force-full 95
Frame Size 95
jumbo frame 95
File Management 96
General Commands 97
boot system 97
copy 98
delete 102
dir 103
whichboot 104
Automatic Code Upgrade Commands 105
upgrade opcode auto 105
upgrade opcode path 106
upgrade opcode reload 107
show upgrade 108
TFTP Configuration Commands 108
ip tftp retry 108
– 7 –
Page 8
Contents
ip tftp timeout 109
show ip tftp 109
Line 110
line 111
databits 111
exec-timeout 112
login 113
parity 114
password 114
password-thresh 115
silent-time 116
speed 117
stopbits 117
timeout login response 118
disconnect 118
terminal 119
show line 120
Event Logging 121
logging command 121
logging facility 122
logging history 122
logging host 123
logging on 124
logging trap 125
clear log 125
show log 126
show logging 127
SMTP Alerts 128
logging sendmail 129
logging sendmail destination-email 129
logging sendmail host 129
logging sendmail level 130
logging sendmail source-email 131
show logging sendmail 131
Time 132
– 8 –
Page 9
Contents
SNTP Commands 133
sntp client 133
sntp poll 134
sntp server 134
show sntp 135
NTP Commands 135
ntp authenticate 135
ntp authentication-key 136
ntp client 137
ntp server 138
show ntp 139
Manual Configuration Commands 139
clock summer-time (date) 139
clock summer-time (predefined) 141
clock summer-time (recurring) 142
clock timezone 143
calendar set 144
show calendar 145
Time Range 145
time-range 146
absolute 146
periodic 147
show time-range 148
Switch Clustering 149
cluster 150
cluster commander 150
cluster ip-pool 151
cluster member 152
rcommand 152
show cluster 153
show cluster members 153
show cluster candidates 154
5 SNMP Commands 155
– 9 –
Page 10
Contents
General SNMP Commands 157
snmp-server 157
snmp-server community 157
snmp-server contact 158
snmp-server location 158
show snmp 159
SNMP Target Host Commands 160
snmp-server enable traps 160
snmp-server host 161
snmp-server enable port-traps link-up-down 163
snmp-server enable port-traps mac-notification 164
show snmp-server enable port-traps 164
SNMPv3 Commands 165
snmp-server engine-id 165
snmp-server group 166
snmp-server user 167
snmp-server view 169
show snmp engine-id 170
show snmp group 170
show snmp user 171
show snmp view 172
Notification Log Commands 173
nlm 173
snmp-server notify-filter 174
show nlm oper-status 175
show snmp notify-filter 175
Additional Trap Commands 176
memory 176
process cpu 177
process cpu guard 177
6 Remote Monitoring Commands 179
rmon alarm 180
rmon event 181
rmon collection history 182
– 10 –
Page 11
Contents
rmon collection rmon1 183
show rmon alarms 184
show rmon events 184
show rmon history 185
show rmon statistics 185
7 Flow Sampling Commands 186
sflow owner 186
sflow polling instance 188
sflow sampling instance 189
show sflow 190
8 Authentication Commands 191
User Accounts and Privilege Levels 192
enable password 192
username 193
privilege 195
show privilege 195
Authentication Sequence 196
authentication enable 196
authentication login 197
RADIUS Client 198
radius-server acct-port 199
radius-server auth-port 199
radius-server host 199
radius-server key 200
radius-server retransmit 201
radius-server timeout 201
show radius-server 202
TACACS+ Client 202
tacacs-server host 203
tacacs-server key 204
tacacs-server port 204
tacacs-server retransmit 205
tacacs-server timeout 205
show tacacs-server 206
– 11 –
Page 12
Contents
AAA 206
aaa accounting commands 207
aaa accounting dot1x 208
aaa accounting exec 209
aaa accounting update 210
aaa authorization commands 210
aaa authorization exec 211
aaa group server 212
server 213
accounting dot1x 213
accounting commands 214
accounting exec 214
authorization commands 215
authorization exec 216
show accounting 216
show authorization 217
Web Server 218
ip http authentication 219
ip http port 219
ip http server 220
ip http secure-port 220
ip http secure-server 221
Telnet Server 222
ip telnet max-sessions 223
ip telnet port 223
ip telnet server 224
telnet (client) 224
show ip telnet 225
Secure Shell 225
ip ssh authentication-retries 228
ip ssh server 228
ip ssh server-key size 229
ip ssh timeout 230
delete public-key 230
ip ssh crypto host-key generate 231
– 12 –
Page 13
Contents
ip ssh crypto zeroize 232
ip ssh save host-key 232
show ip ssh 233
show public-key 233
show ssh 234
802.1X Port Authentication 235
General Commands 236
dot1x default 236
dot1x system-auth-control 236
Authenticator Commands 237
dot1x intrusion-action 237
dot1x max-reauth-req 238
dot1x max-req 238
dot1x operation-mode 239
dot1x port-control 240
dot1x re-authentication 240
dot1x timeout quiet-period 241
dot1x timeout re-authperiod 241
dot1x timeout supp-timeout 242
dot1x timeout tx-period 242
dot1x re-authenticate 243
Supplicant Commands 243
dot1x timeout auth-period 243
dot1x timeout held-period 244
Information Display Commands 244
show dot1x 244
Management IP Filter 247
management 247
show management 248
9 General Security Measures 250
Port Security 251
mac-learning 251
port security 252
show port security 254
– 13 –
Page 14
Contents
Network Access (MAC Address Authentication) 256
network-access aging 257
network-access mac-filter 257
mac-authentication reauth-time 258
network-access dynamic-qos 259
network-access dynamic-vlan 260
network-access guest-vlan 261
network-access max-mac-count 261
network-access mode mac-authentication 262
network-access port-mac-filter 263
mac-authentication intrusion-action 264
mac-authentication max-mac-count 264
clear network-access 265
show network-access 265
show network-access mac-address-table 266
show network-access mac-filter 267
Web Authentication 267
web-auth login-attempts 268
web-auth quiet-period 269
web-auth session-timeout 269
web-auth system-auth-control 270
web-auth 270
web-auth re-authenticate (Port) 271
web-auth re-authenticate (IP) 271
show web-auth 272
show web-auth interface 272
show web-auth summary 273
DHCPv4 Snooping 273
ip dhcp snooping 274
ip dhcp snooping information option 276
ip dhcp snooping information option encode no-subtype 278
ip dhcp snooping information option remote-id 279
ip dhcp snooping information option tr101 board-id 280
ip dhcp snooping information policy 280
ip dhcp snooping verify mac-address 281
– 14 –
Page 15
Contents
ip dhcp snooping vlan 282
ip dhcp snooping information option circuit-id 283
ip dhcp snooping trust 284
ip dhcp snooping max-number 285
ip dhcp snooping trust 286
clear ip dhcp snooping binding 287
clear ip dhcp snooping database flash 287
ip dhcp snooping database flash 288
show ip dhcp snooping 288
show ip dhcp snooping binding 289
IPv4 Source Guard 289
ip source-guard binding 290
ip source-guard 292
ip source-guard max-binding 293
ip source-guard mode 294
clear ip source-guard binding blocked 295
show ip source-guard 296
show ip source-guard binding 296
ARP Inspection 297
ip arp inspection 298
ip arp inspection filter 299
ip arp inspection log-buffer logs 300
ip arp inspection validate 301
ip arp inspection vlan 301
ip arp inspection limit 302
ip arp inspection trust 303
show ip arp inspection configuration 304
show ip arp inspection interface 304
show ip arp inspection log 305
show ip arp inspection statistics 305
show ip arp inspection vlan 305
Denial of Service Protection 306
dos-protection echo-chargen 307
dos-protection smurf 307
dos-protection tcp-flooding 308
– 15 –
Page 16
Contents
dos-protection tcp-null-scan 308
dos-protection tcp-syn-fin-scan 309
dos-protection tcp-xmas-scan 309
dos-protection udp-flooding 310
dos-protection win-nuke 310
show dos-protection 311
Port-based Traffic Segmentation 311
traffic-segmentation 312
traffic-segmentation session 313
traffic-segmentation uplink/downlink 314
traffic-segmentation uplink-to-uplink 315
show traffic-segmentation 315
10 Access Control Lists 317
IPv4 ACLs 317
access-list ip 318
permit, deny (Standard IP ACL) 319
permit, deny (Extended IPv4 ACL) 320
ip access-group 322
show ip access-group 323
show ip access-list 323
IPv6 ACLs 324
access-list ipv6 324
permit, deny (Standard IPv6 ACL) 325
permit, deny (Extended IPv6 ACL) 326
ipv6 access-group 329
show ipv6 access-group 330
show ipv6 access-list 330
MAC ACLs 331
access-list mac 331
permit, deny (MAC ACL) 332
mac access-group 334
show mac access-group 335
show mac access-list 335
ARP ACLs 336
– 16 –
Page 17
Contents
access-list arp 336
permit, deny (ARP ACL) 337
show access-list arp 338
ACL Information 339
clear access-list hardware counters 339
show access-group 340
show access-list 340
11 Interface Commands 342
Interface Configuration 343
interface 343
capabilities 344
description 345
flowcontrol 346
history 347
media-type 347
negotiation 348
shutdown 349
speed-duplex 349
clear counters 350
show interfaces brief 351
show interfaces counters 352
show interfaces history 355
show interfaces status 357
show interfaces switchport 358
Transceiver Threshold Configuration 359
transceiver-monitor 359
transceiver-threshold-auto 360
transceiver-threshold current 360
transceiver-threshold rx-power 361
transceiver-threshold temperature 362
transceiver-threshold tx-power 363
transceiver-threshold voltage 364
show interfaces transceiver 365
show interfaces transceiver-threshold 366
– 17 –
Page 18
Contents
Cable Diagnostics 367
test cable-diagnostics 367
show cable-diagnostics 368
Power Savings 369
power-save 369
show power-save 370
12 Link Aggregation Commands 372
Manual Configuration Commands 373
port channel load-balance 373
channel-group 375
Dynamic Configuration Commands 375
lacp 375
lacp admin-key (Ethernet Interface) 377
lacp port-priority 378
lacp system-priority 379
lacp admin-key (Port Channel) 380
lacp timeout 380
Trunk Status Display Commands 381
show lacp 381
show port-channel load-balance 385
13 Port Mirroring Commands 386
Local Port Mirroring Commands 386
port monitor 386
show port monitor 387
RSPAN Mirroring Commands 388
rspan source 390
rspan destination 391
rspan remote vlan 392
no rspan session 393
show rspan 394
14 Congestion Control Commands 395
Rate Limit Commands 395
rate-limit 395
– 18 –
Page 19
Contents
Storm Control Commands 396
switchport packet-rate 397
15 Loopback Detection Commands 398
loopback-detection 399
loopback-detection action 399
loopback-detection recover-time 400
loopback-detection transmit-interval 401
loopback detection trap 401
loopback-detection release 402
show loopback-detection 402
16 Address Table Commands 404
mac-address-table aging-time 404
mac-address-table static 405
clear collision-mac-address-table 406
clear mac-address-table dynamic 406
show collision-mac-address-table 406
show mac-address-table 407
show mac-address-table aging-time 408
show mac-address-table count 408
17 Spanning Tree Commands 410
spanning-tree 411
spanning-tree cisco-prestandard 412
spanning-tree forward-time 413
spanning-tree hello-time 413
spanning-tree max-age 414
spanning-tree mode 415
spanning-tree mst configuration 416
spanning-tree pathcost method 416
spanning-tree priority 417
spanning-tree system-bpdu-flooding 418
spanning-tree tc-prop 418
spanning-tree transmission-limit 419
max-hops 420
– 19 –
Page 20
Contents
mst priority 420
mst vlan 421
name 422
revision 422
spanning-tree bpdu-filter 423
spanning-tree bpdu-guard 424
spanning-tree cost 425
spanning-tree edge-port 426
spanning-tree link-type 427
spanning-tree loopback-detection 428
spanning-tree loopback-detection action 428
spanning-tree loopback-detection release-mode 429
spanning-tree loopback-detection trap 430
spanning-tree mst cost 430
spanning-tree mst port-priority 431
spanning-tree port-bpdu-flooding 432
spanning-tree port-priority 433
spanning-tree root-guard 433
spanning-tree spanning-disabled 434
spanning-tree tc-prop-stop 435
spanning-tree loopback-detection release 435
spanning-tree protocol-migration 436
show spanning-tree 437
show spanning-tree mst configuration 439
show spanning-tree tc-prop 439
18 VLAN Commands 441
Editing VLAN Groups 441
vlan database 442
vlan 442
Configuring VLAN Interfaces 443
interface vlan 444
switchport acceptable-frame-types 445
switchport allowed vlan 445
switchport ingress-filtering 446
– 20 –
Page 21
Contents
switchport mode 447
switchport native vlan 448
Displaying VLAN Information 449
show vlan 449
Configuring IEEE 802.1Q Tunneling 450
dot1q-tunnel system-tunnel-control 451
switchport dot1q-tunnel mode 452
switchport dot1q-tunnel priority map 453
switchport dot1q-tunnel service match cvid 453
switchport dot1q-tunnel tpid 455
show dot1q-tunnel 456
Configuring Protocol-based VLANs 457
protocol-vlan protocol-group (Configuring Groups) 458
protocol-vlan protocol-group (Configuring Interfaces) 459
show protocol-vlan protocol-group 460
show interfaces protocol-vlan protocol-group 461
Configuring MAC Based VLANs 461
mac-vlan 462
show mac-vlan 463
Configuring Voice VLANs 463
voice vlan 464
voice vlan aging 465
voice vlan mac-address 466
switchport voice vlan 467
switchport voice vlan priority 468
switchport voice vlan rule 468
switchport voice vlan security 469
show voice vlan 469
19 Class of Service Commands 471
Priority Commands (Layer 2) 471
queue mode 472
queue weight 473
switchport priority default 474
show queue mode 475
– 21 –
Page 22
Contents
show queue weight 475
Priority Commands (Layer 3 and 4) 476
qos map cos-queue 476
qos map dscp-queue 478
qos map trust-mode 479
show qos map cos-queue 480
show qos map dscp-queue 480
show qos map trust-mode 481
20 Quality of Service Commands 483
class-map 484
description 485
match 485
rename 486
policy-map 487
class 488
police rate 489
set cos 490
service-policy 491
show class-map 491
show policy-map 492
show policy-map interface 493
21 Multicast Filtering Commands 494
IGMP Snooping 494
ip igmp snooping 496
ip igmp snooping priority 496
ip igmp snooping proxy-reporting 497
ip igmp snooping querier 498
ip igmp snooping router-alert-option-check 498
ip igmp snooping router-port-expire-time 499
ip igmp snooping tcn-flood 499
ip igmp snooping tcn-query-solicit 501
ip igmp snooping unregistered-data-flood 501
ip igmp snooping unsolicited-report-interval 502
ip igmp snooping version 503
– 22 –
Page 23
Contents
ip igmp snooping version-exclusive 503
ip igmp snooping vlan general-query-suppression 504
ip igmp snooping vlan immediate-leave 505
ip igmp snooping vlan last-memb-query-count 506
ip igmp snooping vlan last-memb-query-intvl 506
ip igmp snooping vlan mrd 507
ip igmp snooping vlan proxy-address 508
ip igmp snooping vlan query-interval 509
ip igmp snooping vlan query-resp-intvl 510
ip igmp snooping vlan static 511
clear ip igmp snooping groups dynamic 511
clear ip igmp snooping statistics 512
show ip igmp snooping 512
show ip igmp snooping group 513
show ip igmp snooping mrouter 514
show ip igmp snooping statistics 515
Static Multicast Routing 518
ip igmp snooping vlan mrouter 518
IGMP Filtering and Throttling 519
ip igmp filter (Global Configuration) 520
ip igmp profile 520
permit, deny 521
range 521
ip igmp filter (Interface Configuration) 522
ip igmp max-groups 523
ip igmp max-groups action 523
ip igmp query-drop 524
ip multicast-data-drop 524
show ip igmp filter 525
show ip igmp profile 526
show ip igmp query-drop 526
show ip igmp throttle interface 527
show ip multicast-data-drop 528
MLD Snooping 528
ipv6 mld snooping 529
– 23 –
Page 24
Contents
ipv6 mld snooping proxy-reporting 530
ipv6 mld snooping querier 530
ipv6 mld snooping query-interval 531
ipv6 mld snooping query-max-response-time 532
ipv6 mld snooping robustness 532
ipv6 mld snooping router-port-expire-time 533
ipv6 mld snooping unknown-multicast mode 533
ipv6 mld snooping unsolicited-report-interval 534
ipv6 mld snooping version 535
ipv6 mld snooping vlan immediate-leave 535
ipv6 mld snooping vlan mrouter 536
ipv6 mld snooping vlan static 536
clear ipv6 mld snooping groups dynamic 537
clear ipv6 mld snooping statistics 537
show ipv6 mld snooping 538
show ipv6 mld snooping group 539
show ipv6 mld snooping group source-list 539
show ipv6 mld snooping mrouter 540
show ipv6 mld snooping statistics 541
MLD Filtering and Throttling 545
ipv6 mld filter (Global Configuration) 546
ipv6 mld profile 546
permit, deny 547
range 547
ipv6 mld filter (Interface Configuration) 548
ipv6 mld max-groups 549
ipv6 mld max-groups action 550
ipv6 mld query-drop 550
show ipv6 mld filter 551
show ipv6 mld profile 551
show ipv6 mld query-drop 552
show ipv6 mld throttle interface 552
22 LLDP Commands 554
lldp 556
– 24 –
Page 25
Contents
lldp holdtime-multiplier 556
lldp med-fast-start-count 557
lldp notification-interval 557
lldp refresh-interval 558
lldp reinit-delay 558
lldp tx-delay 559
lldp admin-status 560
lldp basic-tlv management-ip-address 560
lldp basic-tlv port-description 561
lldp basic-tlv system-capabilities 562
lldp basic-tlv system-description 562
lldp basic-tlv system-name 563
lldp dot1-tlv proto-ident 563
lldp dot1-tlv proto-vid 564
lldp dot1-tlv pvid 564
lldp dot1-tlv vlan-name 565
lldp dot3-tlv link-agg 565
lldp dot3-tlv mac-phy 566
lldp dot3-tlv max-frame 566
lldp med-location civic-addr 567
lldp med-notification 568
lldp med-tlv inventory 569
lldp med-tlv location 570
lldp med-tlv med-cap 570
lldp med-tlv network-policy 571
lldp notification 571
show lldp config 572
show lldp info local-device 573
show lldp info remote-device 574
show lldp info statistics 576
23 Domain Name Service Commands 578
DNS Commands 578
ip domain-list 578
ip domain-lookup 580
– 25 –
Page 26
Contents
ip domain-name 581
ip host 581
ip name-server 582
ipv6 host 583
clear dns cache 584
clear host 584
show dns 585
show dns cache 585
show hosts 586
Multicast DNS Commands 586
ip mdns 586
show ip mdns 587
24 DHCP Commands 588
DHCP Client 588
DHCP for IPv4 589
ip dhcp dynamic-provision 589
ip dhcp client class-id 590
ip dhcp restart client 592
show ip dhcp dynamic-provision 592
DHCP for IPv6 593
ipv6 dhcp client rapid-commit vlan 593
ipv6 dhcp restart client vlan 594
show ipv6 dhcp duid 595
show ipv6 dhcp vlan 595
DHCP Relay 596
ip dhcp relay server 596
ip dhcp restart relay 597
25 IP Interface Commands 599
IPv4 Interface 599
Basic IPv4 Configuration 600
ip address 600
ip default-gateway 602
show ip default-gateway 603
show ip interface 603
– 26 –
Page 27
Contents
show ip traffic 604
traceroute 605
ping 606
ARP Configuration 607
arp 607
ip proxy-arp 608
clear arp-cache 609
show arp 609
IPv6 Interface 610
Interface Address Configuration and Utilities 611
ipv6 default-gateway 611
ipv6 address 612
ipv6 address autoconfig 613
ipv6 address eui-64 615
ipv6 address link-local 617
ipv6 enable 618
ipv6 mtu 619
show ipv6 default-gateway 620
show ipv6 interface 620
show ipv6 mtu 623
show ipv6 traffic 623
clear ipv6 traffic 628
ping6 628
traceroute6 629
Neighbor Discovery 631
ipv6 nd dad attempts 631
ipv6 nd ns-interval 632
ipv6 nd reachable-time 634
clear ipv6 neighbors 635
show ipv6 neighbors 635
26 IP Routing Commands 637
Global Routing Configuration 637
IPv4 Commands 637
ip route 637
– 27 –
Page 28
Contents
show ip route 638
SECTION III APPENDICES 641
A Troubleshooting 642
Problems Accessing the Management Interface 642
Using System Logs 643
B License Information 644
The GNU General Public License 644
Glossary 648
Commands 656
Index 662
– 28 –
Page 29
Tables
Table 1: Options 60, 66 and 67 Statements 55
Table 2: Options 55 and 124 Statements 55
Table 1: General Command Modes 67
Table 2: Configuration Command Modes 69
Table 3: Keystroke Commands 69
Table 4: Command Group Index 71
Table 5: General Commands 73
Table 6: System Management Commands 81
Table 7: Device Designation Commands 81
Table 8: System Status Commands 82
Table 9: show access-list tcam-utilization - display description 84
Table 10: show process cpu guard - display description 86
Table 11: show system – display description 91
Table 12: show version – display description 94
Table 13: Fan Control Commands 95
Table 14: Frame Size Commands 95
Table 15: Flash/File Commands 97
Table 16: File Directory Information 104
Table 17: Line Commands 110
Table 18: Event Logging Commands 121
Table 19: Logging Levels 123
Table 20: show logging flash/ram - display description 127
Table 21: show logging trap - display description 128
Table 22: Event Logging Commands 128
Table 23: Time Commands 132
Table 24: Predefined Summer-Time Parameters 141
Table 25: Time Range Commands 145
Table 26: Switch Cluster Commands 149
Table 27: SNMP Commands 155
– 29 –
Page 30
Contents
Table 28: show snmp engine-id - display description 170
Table 29: show snmp group - display description 171
Table 30: show snmp user - display description 172
Table 31: show snmp view - display description 173
Table 32: RMON Commands 179
Table 33: sFlow Commands 186
Table 34: Authentication Commands 191
Table 35: User Access Commands 192
Table 36: Default Login Settings 194
Table 37: Authentication Sequence Commands 196
Table 38: RADIUS Client Commands 198
Table 39: TACACS+ Client Commands 203
Table 40: AAA Commands 206
Table 41: Web Server Commands 218
Table 42: HTTPS System Support 222
Table 43: Telnet Server Commands 222
Table 44: Secure Shell Commands 225
Table 45: show ssh - display description 234
Table 46: 802.1X Port Authentication Commands 235
Table 47: Management IP Filter Commands 247
Table 48: General Security Commands 250
Table 49: Management IP Filter Commands 251
Table 50: show port security - display description 255
Table 51: Network Access Commands 256
Table 52: Dynamic QoS Profiles 259
Table 53: Web Authentication 268
Table 54: DHCP Snooping Commands 273
Table 55: Option 82 information 278
Table 56: Option 82 information 283
Table 57: IPv4 Source Guard Commands 289
Table 58: ARP Inspection Commands 297
Table 59: DoS Protection Commands 306
Table 60: Commands for Configuring Traffic Segmentation 311
Table 61: Traffic Segmentation Forwarding 312
Table 62: Access Control List Commands 317
– 30 –
Page 31
Contents
Table 63: IPv4 ACL Commands 317
Table 64: IPv6 ACL Commands 324
Table 65: MAC ACL Commands 331
Table 66: ARP ACL Commands 336
Table 67: ACL Information Commands 339
Table 68: Interface Commands 342
Table 69: show interfaces counters - display description 353
Table 70: show interfaces switchport - display description 359
Table 71: Link Aggregation Commands 372
Table 72: show lacp counters - display description 382
Table 73: show lacp internal - display description 383
Table 74: show lacp neighbors - display description 384
Table 75: show lacp sysid - display description 384
Table 76: Port Mirroring Commands 386
Table 77: Mirror Port Commands 386
Table 78: RSPAN Commands 388
Table 79: Congestion Control Commands 395
Table 80: Rate Limit Commands - Interface 395
Table 81: Rate Limit Commands - Storm Control 396
Table 82: Loopback Detection Commands 398
Table 83: Address Table Commands 404
Table 84: Spanning Tree Commands 410
Table 85: Recommended STA Path Cost Range 425
Table 86: Default STA Path Costs 425
Table 87: VLAN Commands 441
Table 88: Commands for Editing VLAN Groups 441
Table 89: Commands for Configuring VLAN Interfaces 443
Table 90: Commands for Displaying VLAN Information 449
Table 91: 802.1Q Tunneling Commands 450
Table 92: Protocol-based VLAN Commands 458
Table 93: MAC Based VLAN Commands 462
Table 94: Voice VLAN Commands 464
Table 95: Priority Commands 471
Table 96: Priority Commands (Layer 2) 471
Table 97: Priority Commands (Layer 3 and 4) 476
– 31 –
Page 32
Contents
Table 98: Default Mapping of CoS/CFI Values to Queue/CFI 477
Table 99: Default Mapping of DSCP/CFI Values to Queue 478
Table 100: Quality of Service Commands 483
Table 101: Multicast Filtering Commands 494
Table 102: IGMP Snooping Commands 494
Table 103: show ip igmp snooping statistics input - display description 515
Table 104: show ip igmp snooping statistics output - display description 516
Table 105: show ip igmp snooping statistics vlan query - display description 517
Table 106: Static Multicast Interface Commands 518
Table 107: IGMP Filtering and Throttling Commands 519
Table 108: MLD Snooping Commands 529
Table 109: show ipv6 MLD snooping statistics input - display description 541
Table 110: show ipv6 MLD snooping statistics output - display description 542
Table 111: show ipv6 MLD snooping statistics query - display description 543
Table 112: show ipv6 MLD snooping statistics summary - display description 544
Table 113: MLD Filtering and Throttling Commands 545
Table 114: LLDP Commands 554
Table 115: LLDP MED Location CA Types 567
Table 116: Address Table Commands 578
Table 117: show dns cache - display description 585
Table 118: show hosts - display description 586
Table 119: DHCP Commands 588
Table 120: DHCP Client Commands 588
Table 121: Options 60, 66 and 67 Statements 591
Table 122: Options 55 and 124 Statements 591
Table 123: DHCP Relay Option 82 Commands 596
Table 124: IP Interface Commands 599
Table 125: IPv4 Interface Commands 599
Table 126: Basic IP Configuration Commands 600
Table 127: Address Resolution Protocol Commands 607
Table 128: IPv6 Configuration Commands 610
Table 129: show ipv6 interface - display description 621
Table 130: show ipv6 mtu - display description 623
Table 131: show ipv6 traffic - display description 625
Table 132: show ipv6 neighbors - display description 636
– 32 –
Page 33
Contents
Table 160: IP Routing Commands 637
Table 161: Global Routing Configuration Commands 637
Table 162: Troubleshooting Chart 642
– 33 –
Page 34
Section I
Getting Started
This section describes how to configure the switch for management access through
the web interface or SNMP.
This section includes these chapters:
◆ "Initial Switch Configuration" on page 35
– 34 –
Page 35
1 Initial Switch Configuration
This chapter includes information on connecting to the switch and basic
configuration procedures.
Connecting to the Switch
This switch series includes a built-in network management agent. The agent
offers a variety of management options, including SNMP, RMON and a webbased interface. A PC may also be connected directly to the switch for
configuration and monitoring via a command line interface (CLI).
Configuration
Options
Note:
change this address, see “Setting an IP Address” on page 39.
The switch’s HTTP web agent allows you to configure switch parameters,
monitor port connections, and display statistics using a standard web browser
such as Internet Explorer 9, Mozilla Firefox 39, or Google Chrome 44, or more
recent versions. The switch’s web management interface can be accessed
from any computer attached to the network.
The CLI program can be accessed by a direct connection to the RS-232 serial
console port on the switch, or remotely by a Telnet connection over the
network.
The switch’s management agent also supports SNMP (Simple Network
Management Protocol). This SNMP agent permits the switch to be managed
from any system in the network using network management software.
The switch’s web interface, console interface, and SNMP agent allow you to
perform the following management functions:
◆ Set user names and passwords
An IPv4 address for this switch is obtained via DHCP by default. To
◆ Set an IP interface for any VLAN
◆ Configure SNMP parameters
◆ Enable/disable any port
◆ Set the speed/duplex mode for any port
◆ Configure the bandwidth of any port by limiting input or output rates
– 35 –
Page 36
Chapter 1
◆ Control port access through IEEE 802.1X security or static address
| Initial Switch Configuration
Connecting to the Switch
filtering
◆ Filter packets using Access Control Lists (ACLs)
◆ Configure up to 4094 IEEE 802.1Q VLANs
◆ Enable GVRP automatic VLAN registration
◆ Configure IP routing for unicast traffic
◆ Configure IGMP multicast filtering
◆ Upload and download system firmware or configuration files via HTTP
(using the web interface) or FTP/SFTP/TFTP (using the command line or
web interface)
◆ Configure Spanning Tree parameters
◆ Configure Class of Service (CoS) priority queuing
◆ Configure static or LACP trunks (up to 8)
◆ Enable port mirroring
Connecting to the
Console Port
◆ Set storm control on any port for excessive broadcast, multicast, or
unknown unicast traffic
◆ Display system information and statistics
The switch provides an RS-232 serial port that enables a connection to a PC
or terminal for monitoring and configuring the switch. A null-modem console
cable is provided with the switch.
Attach a VT100-compatible terminal, or a PC running a terminal emulation
program to the switch. You can use the console cable provided with this
package, or use a null-modem cable that complies with the wiring
assignments shown in the Installation Guide.
To connect a terminal to the console port, complete the following steps:
1. Connect the console cable to the serial port on a terminal, or a PC running
terminal emulation software, and tighten the captive retaining screws on the
DB-9 connector.
2. Connect the other end of the cable to the RS-45 serial port on the switch.
3. Make sure the terminal emulation software is set as follows:
■
Select the appropriate serial port (COM port 1 or COM port 2).
■
Set the baud rate to 115200 bps.
■
Set the data format to 8 data bits, 1 stop bit, and no parity.
■
Set flow control to none.
■
Set the emulation mode to VT100.
– 36 –
Page 37
Chapter 1
■
When using HyperTerminal, select Terminal keys, not Windows keys.
| Initial Switch Configuration
Connecting to the Switch
4. Power on the switch.
After the system completes the boot cycle, the logon screen appears.
Logging Onto the
Command Line
Interface
The CLI program provides two different command levels — normal access
level (Normal Exec) and privileged access level (Privileged Exec). The
commands available at the Normal Exec level are a limited subset of those
available at the Privileged Exec level and allow you to only display information
and use basic utilities. To fully configure the switch parameters, you must
access the CLI at the Privileged Exec level.
Access to both CLI levels are controlled by user names and passwords. The
switch has a default user name and password for each level. To log into the
CLI at the Privileged Exec level using the default user name and password,
perform these steps:
1. To initiate your console connection, press <Enter>. The “User Access
Verification” procedure starts.
2. At the User Name prompt, enter “admin.”
3. At the Password prompt, also enter “admin.” (The password characters are not
displayed on the console screen.)
4. The session is opened and the CLI displays the “Console#” prompt indicating
you have access at the Privileged Exec level.
Setting Passwords If this is your first time to log into the CLI program, you should define new
passwords for both default user names using the “username” command,
record them and put them in a safe place.
Passwords can consist of up to 32 alphanumeric characters and are case
sensitive. To prevent unauthorized access to the switch, set the passwords as
follows:
1. Open the console interface with the default user name and password “admin”
to access the Privileged Exec level.
2. Type “configure” and press <Enter>.
3. Type “username guest password 0 password,” for the Normal Exec level, where
password is your new password. Press <Enter>.
– 37 –
Page 38
Chapter 1
| Initial Switch Configuration
Connecting to the Switch
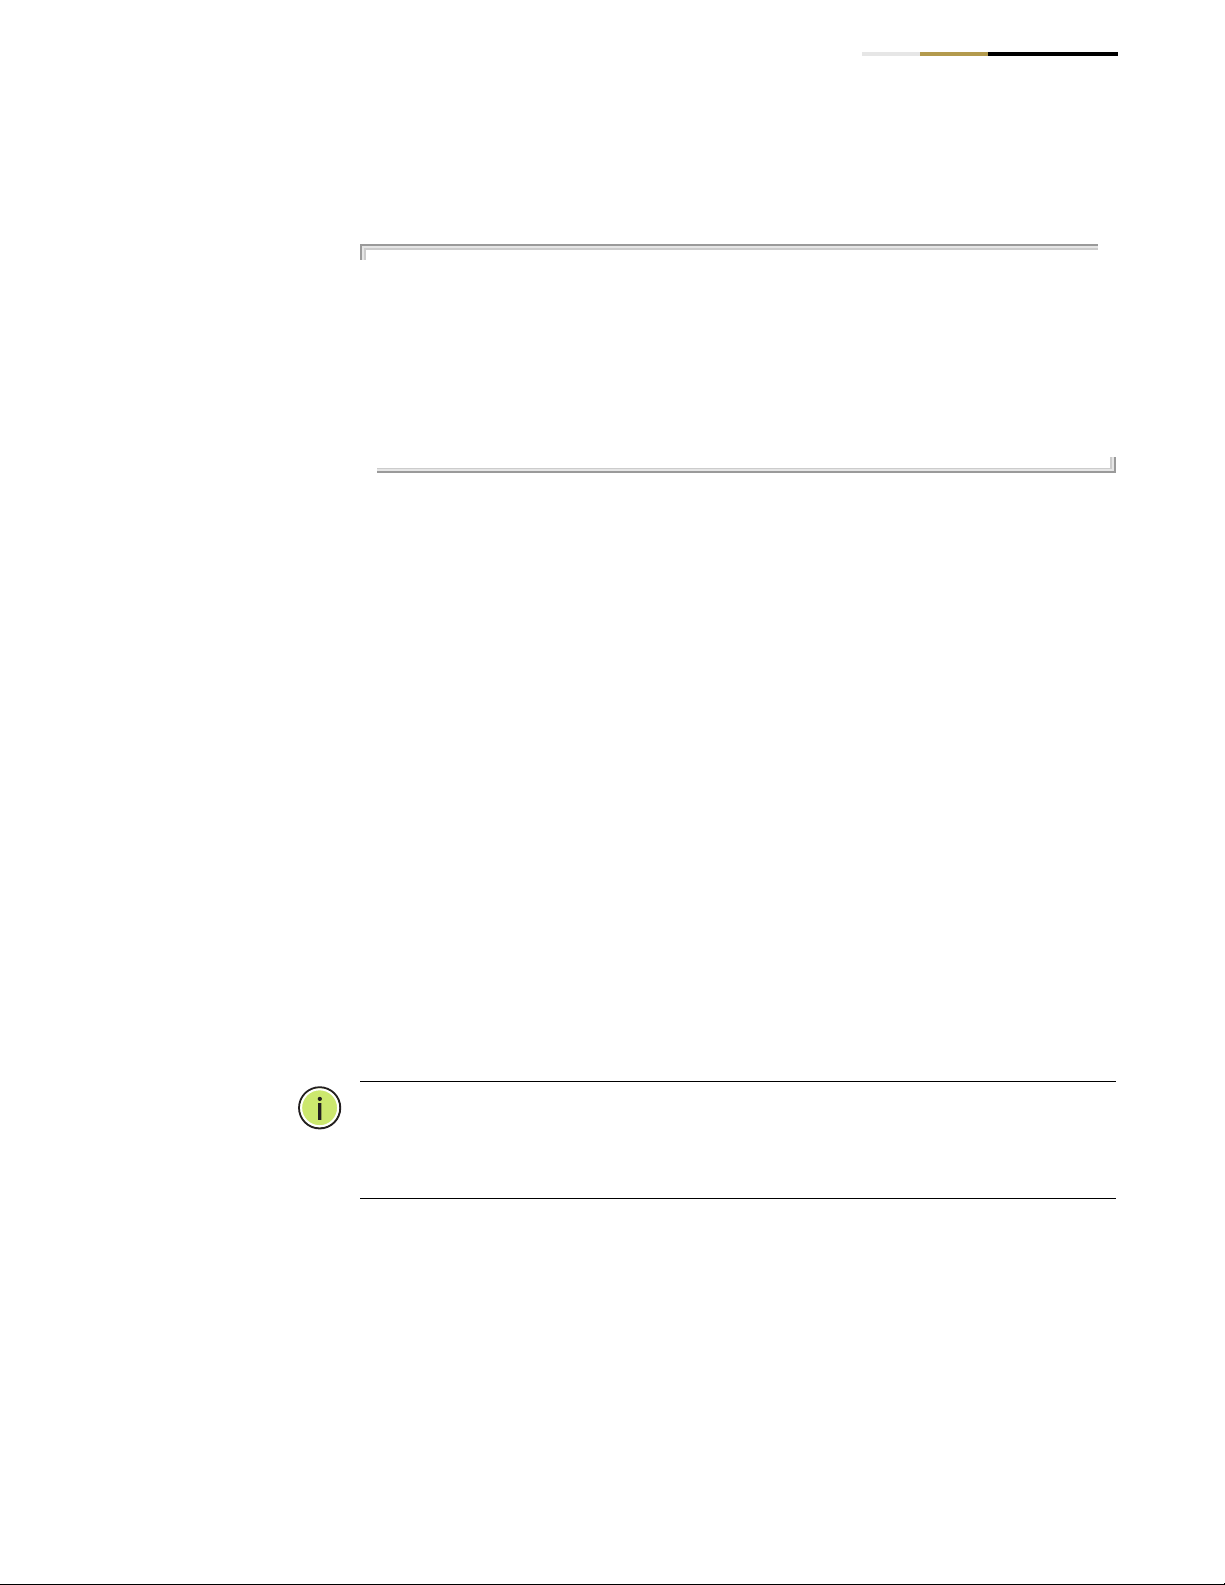
4. Type “username admin password 0 password,” for the Privileged Exec level,
where password is your new password. Press <Enter>.
Username: admin
Password:
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Console#configure
Console(config)#username guest password 0 [password]
Console(config)#username admin password 0 [password]
Console(config)#
* This manual covers the SC30010 Gigabit Ethernet switch. Other than the
difference in port types, there are no significant differences.
Remote
Connections
Prior to accessing the switch’s onboard agent via a network connection, you
must first configure it with a valid IPv4 or IPv6 address, subnet mask, and
default gateway using a console connection, BOOTP or DHCP protocol. To
configure this device as the default gateway, use the ip default-gateway
command.
An IPv4 address for the switch is obtained via DHCP by default. To manually
configure this address or enable dynamic address assignment via DHCP, see
“Setting an IP Address” on page 39.
After configuring the switch’s IP parameters, you can access the onboard
configuration program from anywhere within the attached network. The
onboard configuration program can be accessed using Telnet or SSH from
any computer attached to the network. The switch can also be managed by
any computer using a web browser (Internet Explorer 6, Mozilla Firefox 4, or
Google Chrome 29, or more recent versions), or from a network computer
using SNMP network management software.
Note:
Note:
This switch supports eight Telnet sessions or SSH sessions.
Any VLAN group can be assigned an IP interface address (page 39) for
managing the switch.
The onboard program only provides access to basic configuration functions.
To access the full range of SNMP management functions, you must use
SNMP-based network management software.
– 38 –
Page 39
Configuring the Switch for Remote Management
Configuring the Switch for Remote Management
Chapter 1
| Initial Switch Configuration
Using the Network
Interface
Setting an IP
Address
The switch can be managed through the operational network, known as inband management. Because in-band management traffic is mixed in with
operational network traffic, it is subject to all of the filtering rules usually
applied to a standard network ports such as ACLs and VLAN tagging. In-band
network management can be accessed via a connection to any network port
(1-52).
You must establish IP address information for a switch to obtain management
access through the network. This can be done in either of the following ways:
Manual — You have to input the information, including IP address and subnet
mask. If your management station is not in the same IP subnet as the switch,
you will also need to specify the default gateway router. To configure this
device as the default gateway, use the ip default-gateway command.
◆ Dynamic — The switch can send IPv4 configuration requests to BOOTP
or DHCP address allocation servers on the network, or automatically
generate a unique IPv6 host address based on the local subnet address
prefix received in router advertisement messages. An IPv6 link local
address for use in a local network can also be dynamically generated as
described in “Obtaining an IPv6 Address” on page 44.
This switch is designed as a router, and therefore does not support DHCP for
IPv6, so an IPv6 global unicast address for use in a network containing more
than one subnet can only be manually configured as described in “Assigning an
IPv6 Address” on page 40.
Manual Configuration
You can manually assign an IP address to the switch. You may also need to
specify a default gateway that resides between this device and management
stations that exist on another network segment. Valid IPv4 addresses consist
of four decimal numbers, 0 to 255, separated by periods. Anything outside this
format will not be accepted by the CLI program.
Note:
255.255.255.255, with no defined default gateway.
The default IPv4 address and subnet mask for VLAN 1 is 192.168.2.10
– 39 –
Page 40
Chapter 1
Configuring the Switch for Remote Management
| Initial Switch Configuration
Assigning an IPv4 Address
Before you can assign an IP address to the switch, you must obtain the
following information from your network administrator:
◆ IP address for the switch
◆ Network mask for this network
◆ Default gateway for the network
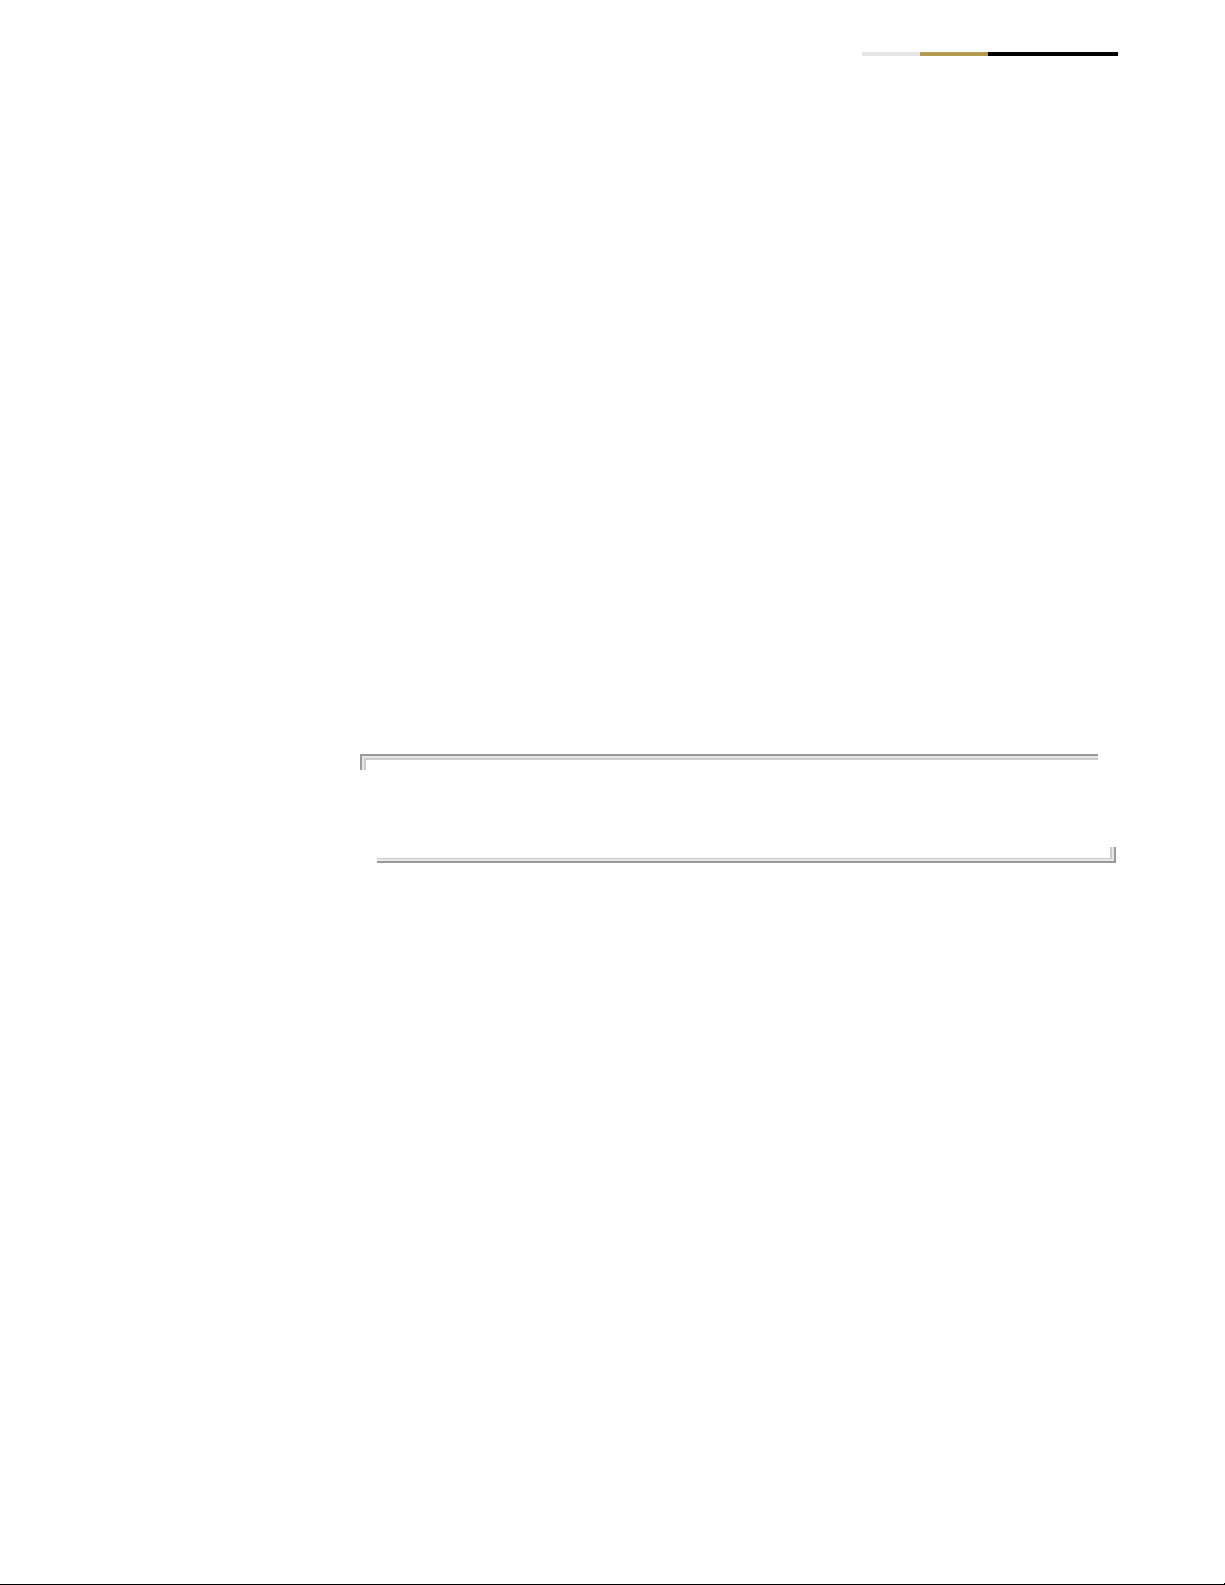
To assign an IPv4 address to the switch, complete the following steps
1. From the Global Configuration mode prompt, type “interface vlan 1” to access
the interface-configuration mode. Press <Enter>.
2. Type “ip address ip-address netmask,” where “ip-address” is the switch IP
address and “netmask” is the network mask for the network. Press <Enter>.
3. Type “exit” to return to the global configuration mode prompt. Press <Enter>.
4. To set the IP address of the default gateway for the network to which the switch
belongs, type “ip default-gateway gateway,” where “gateway” is the IP address
of the default gateway. Press <Enter>.
Console(config)#interface vlan 1
Console(config-if)#ip address 192.168.1.5 255.255.255.0
Console(config-if)#exit
Console(config)#ip default-gateway 192.168.1.254
Assigning an IPv6 Address
This section describes how to configure a “link local” address for connectivity
within the local subnet only, and also how to configure a “global unicast” address,
including a network prefix for use on a multi-segment network and the host
portion of the address.
An IPv6 prefix or address must be formatted according to RFC 2373 “IPv6
Addressing Architecture,” using 8 colon-separated 16-bit hexadecimal values.
One double colon may be used to indicate the appropriate number of zeros
required to fill the undefined fields. For detailed information on the other ways
to assign IPv6 addresses, see “IPv6 Interface” on page 610.
Link Local Address — All link-local addresses must be configured with a prefix
in the range of FE80~FEBF. Remember that this address type makes the
switch accessible over IPv6 for all devices attached to the same local subnet
only. Also, if the switch detects that the address you configured conflicts with
that in use by another device on the subnet, it will stop using the address in
question, and automatically generate a link local address that does not conflict
with any other devices on the local subnet.
– 40 –
Page 41
Chapter 1
| Initial Switch Configuration
Configuring the Switch for Remote Management
To configure an IPv6 link local address for the switch, complete the following
steps:
1. From the Global Configuration mode prompt, type “interface vlan 1” to access
the interface-configuration mode. Press <Enter>.
2. Type “ipv6 address” followed by up to 8 colon-separated 16-bit hexadecimal
values for the ipv6-address similar to that shown in the example, followed by
the “link-local” command parameter. Then press <Enter>.
Console(config)#interface vlan 1
Console(config-if)#ipv6 address FE80::260:3EFF:FE11:6700 link-local
Console(config-if)#ipv6 enable
Console(config-if)#end
Console#show ipv6 interface
VLAN 1 is up
IPv6 is enabled.
Link-local address:
fe80::260:3eff:fe11:6700%1/64
Global unicast address(es):
(None)
Joined group address(es):
ff02::1:ff11:6700
ff02::1
IPv6 link MTU is 1500 bytes
ND DAD is enabled, number of DAD attempts: 3.
ND retransmit interval is 1000 milliseconds
ND advertised retransmit interval is 0 milliseconds
ND reachable time is 30000 milliseconds
ND advertised reachable time is 0 milliseconds
ND advertised router lifetime is 1800 seconds
Console#
Address for Multi-segment Network — Before you can assign an IPv6 address
to the switch that will be used to connect to a multi-segment network, you must
obtain the following information from your network administrator:
◆ Prefix for this network
◆ IP address for the switch
◆ Default gateway for the network
For networks that encompass several different subnets, you must define the
full address, including a network prefix and the host address for the switch.
You can specify either the full IPv6 address, or the IPv6 address and prefix
length. The prefix length for an IPv6 network is the number of bits (from the
left) of the prefix that form the network address, and is expressed as a decimal
number. For example, all IPv6 addresses that start with the first byte of 73
(hexadecimal) could be expressed as 73:0:0:0:0:0:0:0/8 or 73::/8.
– 41 –
Page 42
Chapter 1
| Initial Switch Configuration
Configuring the Switch for Remote Management
To generate an IPv6 global unicast address for the switch, complete the
following steps:
1. From the global configuration mode prompt, type “interface vlan 1” to access
the interface-configuration mode. Press <Enter>.
2. From the interface prompt, type “ipv6 address ipv6-address” or “ipv6 address
ipv6-address/prefix-length,” where “prefix-length” indicates the address bits
used to form the network portion of the address. (The network address starts
from the left of the prefix and should encompass some of the ipv6-address
bits.) The remaining bits are assigned to the host interface. Press <Enter>.
3. Type “exit” to return to the global configuration mode prompt. Press <Enter>.
4. To set the IP address of the IPv6 default gateway for the network to which the
switch belongs, type “ipv6 default-gateway gateway,” where “gateway” is the
IPv6 address of the default gateway. Press <Enter>.
Console(config)#interface vlan 1
Console(config-if)#ipv6 address 2001:DB8:2222:7272::/64
Console(config-if)#exit
Console(config)#ipv6 default-gateway 2001:DB8:2222:7272::254
Console(config)end
Console#show ipv6 interface
VLAN 1 is Administrative Up - Link Up
Address is 00-E0-0C-00-00-FD
Index: 1001, MTU: 1500
Address Mode is DHCP
IPv6 is enabled.
Link-local address:
fe80::260:3eff:fe11:6700%1/64
Global unicast address(es):
2001:db8:2222:7272::/64, subnet is 2001:db8:2222:7272::/64
Joined group address(es):
ff02::1:ff00:0
ff02::1:ff11:6700
ff02::1
IPv6 link MTU is 1500 bytes
ND DAD is enabled, number of DAD attempts: 3.
ND retransmit interval is 1000 milliseconds
ND advertised retransmit interval is 0 milliseconds
ND reachable time is 30000 milliseconds
ND advertised reachable time is 0 milliseconds
ND advertised router lifetime is 1800 seconds
Console#show ipv6 default-gateway
IPv6 default gateway 2001:db8:2222:7272::254
Console#
– 42 –
Page 43
Chapter 1
Configuring the Switch for Remote Management
| Initial Switch Configuration
Dynamic Configuration
Obtaining an IPv4 Address
If you select the “bootp” or “dhcp” option, the system will immediately start
broadcasting service requests. IP will be enabled but will not function until a
BOOTP or DHCP reply has been received. Requests are broadcast every few
minutes using exponential backoff until IP configuration information is
obtained from a BOOTP or DHCP server. BOOTP and DHCP values can
include the IP address, subnet mask, and default gateway. If the DHCP/
BOOTP server is slow to respond, you may need to use the “ip dhcp restart
client” command to re-start broadcasting service requests.
Note that the “ip dhcp restart client” command can also be used to start
broadcasting service requests for all VLANs configured to obtain address
assignments through BOOTP or DHCP. It may be necessary to use this
command when DHCP is configured on a VLAN, and the member ports which
were previously shut down are now enabled.
If the “bootp” or “dhcp” option is saved to the startup-config file (step 6), then
the switch will start broadcasting service requests as soon as it is powered on.
To automatically configure the switch by communicating with BOOTP or
DHCP address allocation servers on the network, complete the following
steps:
1. From the Global Configuration mode prompt, type “interface vlan 1” to access
the interface-configuration mode. Press <Enter>.
2. At the interface-configuration mode prompt, use one of the following
commands:
■
To obtain IP settings via DHCP, type “ip address dhcp” and press <Enter>.
■
To obtain IP settings via BOOTP, type “ip address bootp” and press <Enter>.
3. Type “end” to return to the Privileged Exec mode. Press <Enter>.
4. Wait a few minutes, and then check the IP configuration settings by typing the
“show ip interface” command. Press <Enter>.
5. Then save your configuration changes by typing “copy running-config startup-
config.” Enter the startup file name and press <Enter>.
– 43 –
Page 44
Chapter 1
| Initial Switch Configuration
Configuring the Switch for Remote Management
Console(config)#interface vlan 1
Console(config-if)#ip address dhcp
Console(config-if)#end
Console#show ip interface
VLAN 1 is Administrative Up - Link Up
Address is 00-E0-0C-00-00-FD
Index: 1001, MTU: 1500
Address Mode is DHCP
IP Address: 192.168.0.4 Mask: 255.255.255.0
Proxy ARP is disabled
DHCP Client Vendor Class ID (text): SC30010
DHCP Relay Server:
Console#copy running-config startup-config
Startup configuration file name []: startup
\Write to FLASH Programming.
\Write to FLASH finish.
Success.
Obtaining an IPv6 Address
Link Local Address — There are several ways to configure IPv6 addresses. The
simplest method is to automatically generate a “link local” address (identified by an
address prefix in the range of FE80~FEBF). This address type makes the switch
accessible over IPv6 for all devices attached to the same local subnet.
To generate an IPv6 link local address for the switch, complete the following
steps:
1. From the Global Configuration mode prompt, type “interface vlan 1” to access
the interface-configuration mode. Press <Enter>.
2. Type “ipv6 enable” and press <Enter>.
Console(config)#interface vlan 1
Console(config-if)#ipv6 enable
Console(config-if)#end
Console#show ipv6 interface
VLAN 1 is up
IPv6 is enabled.
Link-local address:
fe80::2e0:cff:fe00:fd%1/64
Global unicast address(es):
2001:db8:2222:7272::/64, subnet is 2001:db8:2222:7272::/64
Joined group address(es):
ff02::1:ff00:0
ff02::1:ff11:6700
ff02::1
IPv6 link MTU is 1500 bytes
ND DAD is enabled, number of DAD attempts: 3.
ND retransmit interval is 1000 milliseconds
ND advertised retransmit interval is 0 milliseconds
ND reachable time is 30000 milliseconds
ND advertised reachable time is 0 milliseconds
ND advertised router lifetime is 1800 seconds
Console#
– 44 –
Page 45
Enabling SNMP Management Access
The switch can be configured to accept management commands from Simple
Network Management Protocol (SNMP) 3rd-party applications. You can configure
the switch to respond to SNMP requests or generate SNMP traps.
When SNMP management stations send requests to the switch (either to
return information or to set a parameter), the switch provides the requested
data or sets the specified parameter. The switch can also be configured to
send information to SNMP managers (without being requested by the
managers) through trap messages, which inform the manager that certain
events have occurred.
The switch includes an SNMP agent that supports SNMP version 1, 2c, and 3
clients. To provide management access for version 1 or 2c clients, you must
specify a community string. The switch provides a default MIB View (i.e., an
SNMPv3 construct) for the default “public” community string that provides read
access to the entire MIB tree, and a default view for the “private” community
string that provides read/write access to the entire MIB tree. However, you
may assign new views to version 1 or 2c community strings that suit your
specific security requirements (see snmp-server view command).
Chapter 1
| Initial Switch Configuration
Enabling SNMP Management Access
Community Strings (for SNMP version 1 and 2c clients)
Community strings are used to control management access to SNMP version
1 and 2c stations, as well as to authorize SNMP stations to receive trap
messages from the switch. You therefore need to assign community strings to
specified users, and set the access level.
The default strings are:
◆ public - with read-only access. Authorized management stations are only
able to retrieve MIB objects.
◆ private - with read/write access. Authorized management stations are
able to both retrieve and modify MIB objects.
To prevent unauthorized access to the switch from SNMP version 1 or 2c
clients, it is recommended that you change the default community strings.
To configure a community string, complete the following steps:
1. From the Privileged Exec level global configuration mode prompt, type “snmp-
server community string mode,” where “string” is the community access string
and “mode” is rw (read/write) or ro (read only). Press <Enter>. (Note that the
default mode is read only.)
2. To remove an existing string, simply type “no snmp-server community string,”
where “string” is the community access string to remove. Press <Enter>.
– 45 –
Page 46
Chapter 1
Console(config)#snmp-server community admin rw
Console(config)#snmp-server community private
Console(config)#
| Initial Switch Configuration
Enabling SNMP Management Access
Note:
If you do not intend to support access to SNMP version 1 and 2c
clients, we recommend that you delete both of the default community strings.
If there are no community strings, then SNMP management access from
SNMP v1 and v2c clients is disabled.
Trap Receivers
You can also specify SNMP stations that are to receive traps from the switch. To
configure a trap receiver, use the “snmp-server host” command. From the
Privileged Exec level global configuration mode prompt, type:
“snmp-server host host-address community-string
[version {1 | 2c | 3 {auth | noauth | priv}}]”
where “host-address” is the IP address for the trap receiver, “communitystring” specifies access rights for a version 1/2c host, or is the user name of a
version 3 host, “version” indicates the SNMP client version, and “auth | noauth
| priv” means that authentication, no authentication, or authentication and
privacy is used for v3 clients. Then press <Enter>. For a more detailed
description of these parameters, see the snmp-server host command. The
following example creates a trap host for each type of SNMP client.
Console(config)#snmp-server host 10.1.19.23 batman
Console(config)#snmp-server host 10.1.19.98 robin version 2c
Console(config)#snmp-server host 10.1.19.34 barbie version 3 auth
Console(config)#
Configuring Access for SNMP Version 3 Clients
To configure management access for SNMPv3 clients, you need to first create a
view that defines the portions of MIB that the client can read or write, assign the
view to a group, and then assign the user to a group. The following example creates
one view called “mib-2” that includes the entire MIB-2 tree branch, and then
another view that includes the IEEE 802.1d bridge MIB. It assigns these respective
read and read/write views to a group call “r&d” and specifies group authentication
via MD5 or SHA. In the last step, it assigns a v3 user to this group, indicating that
MD5 will be used for authentication, provides the password “greenpeace” for
authentication, and the password “einstien” for encryption.
Console(config)#snmp-server view mib-2 1.3.6.1.2.1 included
Console(config)#snmp-server view 802.1d 1.3.6.1.2.1.17 included
Console(config)#snmp-server group r&d v3 auth read mib-2 write 802.1d
Console(config)#snmp-server user steve group r&d v3 auth md5 greenpeace priv
des56 einstien
Console(config)#
– 46 –
Page 47
For a more detailed explanation on how to configure the switch for access
from SNMP v3 clients, refer to “SNMP Commands” on page 155 or to the Web
Management Guide.
Managing System Files
The switch’s flash memory supports three types of system files that can be
managed by the CLI program, the web interface, or SNMP. The switch’s file system
allows files to be uploaded and downloaded, copied, deleted, and set as a start-up
file.
The types of files are:
◆ Configuration — This file type stores system configuration information
and is created when configuration settings are saved. Saved configuration
files can be selected as a system start-up file or can be uploaded via FTP/
SFTP/TFTP to a server for backup. The file named
“Factory_Default_Config.cfg” contains all the system default settings and
cannot be deleted from the system. If the system is booted with the factory
default settings, the switch will also create a file named “startup1.cfg” that
contains system settings for switch initialization, including information
about the unit identifier, and MAC address for the switch. The configuration
settings from the factory defaults configuration file are copied to this file,
which is then used to boot the switch. See “Saving or Restoring
Configuration Settings” on page 48 for more information.
Chapter 1
| Initial Switch Configuration
Managing System Files
◆ Operation Code — System software that is executed after boot-up, also
known as run-time code. This code runs the switch operations and
provides the CLI and web management interfaces.
◆ Diagnostic Code — Software that is run during system boot-up, also
known as POST (Power On Self-Test).
Note:
The Boot ROM and Loader cannot be uploaded or downloaded from
the FTP/SFTP/TFTP server. You must follow the instructions in the release
notes for new firmware, or contact your distributor for help.
Due to the size limit of the flash memory, the switch supports only two
operation code files. However, you can have as many diagnostic code files
and configuration files as available flash memory space allows. The switch
has a total of 128 Mbytes of flash memory for system files.
In the system flash memory, one file of each type must be set as the start-up
file. During a system boot, the diagnostic and operation code files set as the
start-up file are run, and then the start-up configuration file is loaded.
Note that configuration files should be downloaded using a file name that
reflects the contents or usage of the file settings. If you download directly to
– 47 –
Page 48
Chapter 1
| Initial Switch Configuration
Managing System Files
the running-config, the system will reboot, and the settings will have to be
copied from the running-config to a permanent file.
Upgrading the
Operation Code
The following example shows how to download new firmware to the switch
and activate it. The TFTP server could be any standards-compliant server
running on Windows or Linux. When downloading from an FTP server, the
logon interface will prompt for a user name and password configured on the
remote server. Note that “anonymous” is set as the default user name.
File names on the switch are case-sensitive. The destination file name should
not contain slashes (\ or /), and the maximum length for file names is 32
characters for files on the switch or 128 characters for files on the server.
(Valid characters: A-Z, a-z, 0-9, “.”, “-”)
Console#copy tftp file
TFTP server ip address: 10.1.0.19
Choose file type:
1. config: 2. opcode: 2
Source file name: m360.bix
Destination file name: m360.bix
\Write to FLASH Programming.
-Write to FLASH finish.
Success.
Console#config
Console(config)#boot system opcode: m360.bix
Console(config)#exit
Console#dir
File Name Type Startup Modified Time Size (bytes)
------------------------------ ------- ------- ------------------- ----------- Unit 1:
SC3-52T_V1.1.10.171.bix OpCode Y 2017-11-01 05:35:52 8622340
Factory_Default_Config.cfg Config N 2017-11-01 05:26:32 477
startup1.cfg Config Y 2017-11-01 05:26:35 2076
startup2.cfg Config N 2017-11-01 05:57:52 1700
------------------------------------------------------------------------------ Free space for user config files: 2617187
Total space: 32 MB
Console#
Saving or Restoring
Configuration
Settings
Configuration commands only modify the running configuration file and are not
saved when the switch is rebooted. To save all your configuration changes in
nonvolatile storage, you must copy the running configuration file to the start-up
configuration file using the “copy” command.
New startup configuration files must have a name specified. File names on the
switch are case-sensitive, can be from 1 to 31 characters, must not contain
slashes (\ or /), and the leading letter of the file name must not be a period (.).
(Valid characters: A-Z, a-z, 0-9, “.”, “-”, “_”)
There can be more than one user-defined configuration file saved in the
switch’s flash memory, but only one is designated as the “startup” file that is
– 48 –
Page 49
Chapter 1
| Initial Switch Configuration
Managing System Files
loaded when the switch boots. The copy running-config startup-config
command always sets the new file as the startup file. To select a previously
saved configuration file, use the boot system config:<filename> command.
The maximum number of saved configuration files depends on available flash
memory. The amount of available flash memory can be checked by using the
dir command.
To save the current configuration settings, enter the following command:
1. From the Privileged Exec mode prompt, type “copy running-config startup-
config” and press <Enter>.
2. Enter the name of the start-up file. Press <Enter>.
Console#copy running-config startup-config
Startup configuration file name []: startup
\Write to FLASH Programming.
\Write to FLASH finish.
Success.
Console#
To restore configuration settings from a backup server, enter the following
command:
1. From the Privileged Exec mode prompt, type “copy tftp startup-config” and
press <Enter>.
2. Enter the address of the TFTP server. Press <Enter>.
3. Enter the name of the startup file stored on the server. Press <Enter>.
4. Enter the name for the startup file on the switch. Press <Enter>.
Console#copy tftp startup-config
TFTP server IP address: 192.168.0.4
Source configuration file name: startup-rd.cfg
Startup configuration file name [startup1.cfg]:
Success.
Console#
– 49 –
Page 50
Chapter 1
Automatic Installation of Operation Code and Configuration Settings
| Initial Switch Configuration
Automatic Installation of Operation Code and Configuration Settings
Downloading
Operation Code
from a File Server
Automatic Operation Code Upgrade can automatically download an operation
code file when a file newer than the currently installed one is discovered on
the file server. After the file is transferred from the server and successfully
written to the file system, it is automatically set as the startup file, and the
switch is rebooted.
Usage Guidelines
◆ If this feature is enabled, the switch searches the defined URL once during
the bootup sequence.
◆ FTP (port 21) and TFTP (port 69) are both supported. Note that the TCP/
UDP port bindings cannot be modified to support servers listening on nonstandard ports.
◆ The host portion of the upgrade file location URL must be a valid IPv4 IP
address. DNS host names are not recognized. Valid IP addresses consist
of four numbers, 0 to 255, separated by periods.
◆ The path to the directory must also be defined. If the file is stored in the
root directory for the FTP/TFTP service, then use the “/” to indicate this
(e.g.,
ftp://192.168.0.1/).
◆ The file name must not be included in the upgrade file location URL. The
file name of the code stored on the remote server must be C-300series.bix (using lower case letters as indicated).
◆ The FTP connection is made with PASV mode enabled. PASV mode is
needed to traverse some fire walls, even if FTP traffic is not blocked.
PASV mode cannot be disabled.
◆ The switch-based search function is case-insensitive in that it will accept a
file name in upper or lower case (i.e., the switch will accept C-300Series.BIX from the server even though C-300-series.bix was requested).
However, keep in mind that the file systems of many operating systems
such as Unix and most Unix-like systems (FreeBSD, NetBSD, OpenBSD,
and most Linux distributions, etc.) are case-sensitive, meaning that two
files in the same directory, c-300_series.bix and C-300_Series.BIX are
considered to be unique files. Thus, if the upgrade file is stored as C-
300_Series.BIX (or even C-300_seRies.bix) on a case-sensitive server,
then the switch (requesting C-300_Series.BIX) will not be upgraded
because the server does not recognize the requested file name and the
stored file name as being equal. A notable exception in the list of casesensitive Unix-like operating systems is Mac OS X, which by default is
– 50 –
Page 51
Chapter 1
Automatic Installation of Operation Code and Configuration Settings
| Initial Switch Configuration
case-insensitive. Please check the documentation for your server’s
operating system if you are unsure of its file system’s behavior.
◆ Note that the switch itself does not distinguish between upper and lower-
case file names, and only checks to see if the file stored on the server is
more recent than the current runtime image.
◆ If two operation code image files are already stored on the switch’s file
system, then the non-startup image is deleted before the upgrade image is
transferred.
◆ The automatic upgrade process will take place in the background without
impeding normal operations (data switching, etc.) of the switch.
◆ During the automatic search and transfer process, the administrator
cannot transfer or update another operation code image, configuration file,
public key, or HTTPS certificate (i.e., no other concurrent file management
operations are possible).
◆ The upgrade operation code image is set as the startup image after it has
been successfully written to the file system.
◆ The switch will send an SNMP trap and make a log entry upon all upgrade
successes and failures.
◆ The switch will immediately restart after the upgrade file is successfully
written to the file system and set as the startup image.
To enable automatic upgrade, enter the following commands:
1. Specify the TFTP or FTP server to check for new operation code.
■
When specifying a TFTP server, the following syntax must be used, where
filedir indicates the path to the directory containing the new image:
tftp://192.168.0.1[/filedir]/
■
When specifying an FTP server, the following syntax must be used, where
filedir indicates the path to the directory containing the new image:
ftp://[username[:password@]]192.168.0.1[/filedir]/
If the user name is omitted, “anonymous” will be used for the connection. If
the password is omitted a null string (“”) will be used for the connection.
If no user name nor password is required for the connection, then the “@”
character cannot be used in the path name.
– 51 –
Page 52
Chapter 1
| Initial Switch Configuration
Automatic Installation of Operation Code and Configuration Settings
This shows how to specify a TFTP server where new code is stored.
Console(config)#upgrade opcode path tftp://192.168.0.1/sm24/
Console(config)#
This shows how to specify an FTP server where new code is stored.
Console(config)#upgrade opcode path ftp://site9:[email protected]/sm24/
Console(config)#
2. Set the switch to automatically reboot and load the new code after the opcode
upgrade is completed.
Console(config)#upgrade opcode reload
Console(config)#
3. Set the switch to automatically upgrade the current operational code when a
new version is detected on the server. When the switch starts up and automatic
image upgrade is enabled by this command, the switch will follow these steps
when it boots up:
a. It will search for a new version of the image at the location specified by
upgrade opcode path command. The name for the new image stored on
the FTP/SFTP/TFTP server must be C-300-series.bix. If the switch detects a
code version newer than the one currently in use, it will download the new
image. If two code images are already stored in the switch, the image not
set to start up the system will be overwritten by the new version.
b. After the image has been downloaded, the switch will send a trap message
to log whether or not the upgrade operation was successful.
c. It sets the new version as the startup image.
d. It then restarts the system to start using the new image.
Console(config)#upgrade opcode auto
Console(config)#
4. Display the automatic upgrade settings.
Console#show upgrade
Auto Image Upgrade Global Settings:
Status : Enabled
Reload Status : Enabled
Path :
File Name : C-300-series.bix
Console#
– 52 –
Page 53
Chapter 1
| Initial Switch Configuration
Automatic Installation of Operation Code and Configuration Settings
The following shows an example of the upgrade process.
Console#dir
File Name Type Startup Modified Time Size (bytes)
------------------------------ ------- ------- ------------------- ----------
- Unit 1:
SC3-52T_V1.1.10.171.bix OpCode Y 2017-11-01 05:35:52 8622340
Factory_Default_Config.cfg Config N 2017-11-01 05:26:32 477
startup1.cfg Config Y 2017-11-01 05:26:35 2076
startup2.cfg Config N 2017-11-01 05:57:52 1700
----------------------------------------------------------------------------
-- Free space for user config files: 2617187
Total space: 32 MB
...
Press ENTER to start session
Automatic Upgrade is looking for a new image
New image detected: current version V1.1.9.4; new version V1.1.10.171
Image upgrade in progress
Downloading new image
Flash programming started
Flash programming completed
Success
The switch will now restart
...
Press ENTER to start session
Automatic Upgrade is looking for a new image
No new image detected
User Access Verification
Specifying a DHCP
Client Identifier
Username: admin
Password:
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Console#dir
File Name Type Startup Modified Time Size (bytes)
------------------------------ ------- ------- ------------------- ----------
- Unit 1:
SC3-52T_V1.1.10.171.bix OpCode Y 2017-11-01 05:35:52 8622340
SC3-52T_V1.1.9.4.bix OpCode N 2017-07-15 07:21:11 8572590
Factory_Default_Config.cfg Config N 2017-11-01 05:26:32 477
startup1.cfg Config Y 2017-11-01 05:26:35 2076
startup2.cfg Config N 2017-11-01 05:57:52 1700
----------------------------------------------------------------------------
-- Free space for user config files: 2617187
Total space: 32 MB
Console#
DHCP servers index their database of address bindings using the client’s
Media Access Control (MAC) Address or a unique client identifier. The client
identifier is used to identify the vendor class and configuration of the switch to
the DHCP server, which then uses this information to decide on how to service
the client or the type of information to return.
– 53 –
Page 54
Chapter 1
Downloading Configuration Files / Other Parameters from a DHCP Server
| Initial Switch Configuration
DHCP client Identifier (Option 60) is used by DHCP clients to specify their
unique identifier. The client identifier is optional and can be specified while
configuring DHCP on the primary network interface. DHCP Option 60 is
disabled by default.
The general framework for this DHCP option is set out in RFC 2132 (Option
60). This information is used to convey configuration settings or other
identification information about a client, but the specific string to use should be
supplied by your service provider or network administrator. Options 60
(vendor-class-identifier), 66 (tftp-server-name) and 67 (bootfile-name)
statements can be added to the server daemon’s configuration file as
described in the following section.
If the DHCP server has an index entry for a switch requesting service, it
should reply with the TFTP server name and boot file name. Note that the
vendor class identifier can be formatted in either text or hexadecimal, but the
format used by both the client and server must be the same.
Console(config)#interface vlan 2
Console(config-if)#ip dhcp client class-id hex 0000e8666572
Console(config-if)#
Downloading Configuration Files / Other Parameters from a DHCP Server
Information passed on to the switch from a DHCP server may also include a
configuration file to be downloaded and the TFTP servers where that file can
be accessed, as well as other parameters. If the Factory Default Configuration
file is used to provision the switch at startup, in addition to requesting IP
configuration settings from the DHCP server, it will also ask for the name of a
bootup configuration file and TFTP servers where that file is stored.
If the switch receives information that allows it to download the remote bootup
file, it will save this file to a local buffer, and then restart the provision process.
Note the following DHCP client behavior:
◆ To enable dynamic provisioning via a DHCP server, this feature must be
enabled using the ip dhcp dynamic-provision command.
◆ The bootup configuration file received from a TFTP server is stored on the
switch with the original file name. If this file name already exists in the
switch, the file is overwritten.
◆ If the name of the bootup configuration file is the same as the Factory
Default Configuration file, the download procedure will be terminated, and
the switch will not send any further DHCP client requests.
– 54 –
Page 55
Chapter 1
Downloading Configuration Files / Other Parameters from a DHCP Server
◆ If the switch fails to download the bootup configuration file based on
| Initial Switch Configuration
information passed by the DHCP server, it will not send any further DHCP
client requests.
◆ If the switch does not receive a DHCP response prior to completing the
bootup process, it will continue to send a DHCP client request once a
minute. These requests will only be terminated if the switch’s address is
manually configured, but will resume if the address mode is set back to
DHCP.
To successfully transmit a bootup configuration file to the switch, the DHCP
daemon (using a Linux based system for this example) must be configured
with the following information:
◆ Options 60, 66 and 67 statements can be added to the daemon’s
configuration file.
Table 1: Options 60, 66 and 67 Statements
Statement
Option
Keyword Parameter
60 vendor-class-identifier a string indicating the vendor class identifier
66 tftp-server-name a string indicating the tftp server name
67 bootfile-name a string indicating the bootfile name
◆ By default, DHCP option 66/67 parameters are not carried in a DHCP
server reply. To ask for a DHCP reply with option 66/67 information, the
DHCP client request sent by this switch includes a “parameter request list”
asking for this information. Besides these items, the client request also
includes a “vendor class identifier” that allows the DHCP server to identify
the device, and select the appropriate configuration file for download. This
information is included in Option 55 and 124.
Table 2: Options 55 and 124 Statements
Statement
Option
Keyword Parameter
55 dhcp-parameter-request-list a list of parameters, separated by a comma ', '
124 vendor-class-identifier a string indicating the vendor class identifier
The following configuration example is provided for a Linux-based DHCP
daemon (dhcpd.conf file). In the “Vendor class” section, the server will always
send Option 66 and 67 to tell the switch to download the “test” configuration
file from server 192.168.255.101.
– 55 –
Page 56
Chapter 1
| Initial Switch Configuration
Setting the System Clock
ddns-update-style ad-hoc;
default-lease-time 600;
max-lease-time 7200;
log-facility local7;
server-name "Server1";
Server-identifier 192.168.255.250;
#option 66, 67
option space dynamicProvision code width 1 length 1 hash size 2;
option dynamicProvision.tftp-server-name code 66 = text;
option dynamicProvision.bootfile-name code 67 = text;
subnet 192.168.255.0 netmask 255.255.255.0 {
range 192.168.255.160 192.168.255.200;
option routers 192.168.255.101;
option tftp-server-name "192.168.255.100"; #Default Option 66
option bootfile-name "bootfile"; #Default Option 67
}
class "Option66,67_1" { #DHCP Option 60 Vendor class
two
match if option vendor-class-identifier = "sc30010.cfg";
option tftp-server-name "192.168.255.101";
option bootfile-name "test";
}
Note:
Use “sc30010.cfg” for the vendor-class-identifier in the dhcpd.conf file.
Setting the System Clock
Simple Network Time Protocol (SNTP) or Network Time Protocol (NTP) can
be used to set the switch’s internal clock based on periodic updates from a
time server. Maintaining an accurate time on the switch enables the system
log to record meaningful dates and times for event entries. You can also
manually set the clock. If the clock is not set manually or via SNTP or NTP, the
switch will only record the time from the factory default set at the last bootup.
When the SNTP client is enabled, the switch periodically sends a request for a
time update to a configured time server. You can configure up to three time
server IP addresses. The switch will attempt to poll each server in the
configured sequence.
The switch also supports the following time settings:
◆ Time Zone – You can specify the offset from Coordinated Universal Time
(UTC), also known as Greenwich Mean Time (GMT).
– 56 –
Page 57
Chapter 1
| Initial Switch Configuration
Setting the System Clock
◆ Summer Time/Daylight Saving Time (DST) – In some regions, the time
shifts by one hour in the fall and spring. The switch supports manual entry
for one-time or recurring clock shifts.
Setting the Time
Manually
To manually set the clock to 14:11:36, April 1st, 2013, enter this command.
Console#calendar set 14 11 36 1 April 2013
Console#
To set the time zone, enter a command similar to the following.
Console(config)#clock timezone Japan hours 8 after-UTC
Console(config)#
To set the time shift for summer time, enter a command similar to the
following.
Console(config)#clock summer-time SUMMER date 2 april 2013 0 0 30 june 2013 0
0
Console(config)#
To display the clock configuration settings, enter the following command.
Console#show calendar
Current Time : Jul 28 00:54:20 2015
Time Zone : Japan, 08:00
Summer Time : SUMMER, offset 60 minutes
Apr 2 2013 00:00 to Jun 30 2015 00:00
Summer Time in Effect : Yes
Console#
Configuring SNTP Setting the clock based on an SNTP server can provide more accurate clock
synchronization across network switches than manually-configured time. To
configure SNTP, set the switch as an SNTP client, and then set the polling
interval, and specify a time server as shown in the following example.
Console(config)#sntp client
Console(config)#sntp poll 60
Console(config)#sntp server 10.1.0.19
Console(config)#exit
Console#show sntp
Current Time : Apr 2 16:06:07 2013
Poll Interval : 60 seconds
Current Mode : Unicast
SNTP Status : Enabled
SNTP Server : 10.1.0.19
Current Server : 10.1.0.19
Console#
– 57 –
Page 58
Chapter 1
| Initial Switch Configuration
Setting the System Clock
Configuring NTP Requesting the time from a an NTP server is the most secure method. You
can enable NTP authentication to ensure that reliable updates are received
from only authorized NTP servers. The authentication keys and their
associated key number must be centrally managed and manually distributed
to NTP servers and clients. The key numbers and key values must match on
both the server and client.
When more than one time server is configured, the client will poll all of the time
servers, and compare the responses to determine the most reliable and
accurate time update for the switch.
To configure NTP time synchronization, enter commands similar to the
following.
Console(config)#ntp client
Console(config)#ntp authentication-key 45 md5 thisiskey45
Console(config)#ntp authenticate
Console(config)#ntp server 192.168.3.20
Console(config)#ntp server 192.168.3.21
Console(config)#ntp server 192.168.5.23 key 19
Console(config)#exit
Console#show ntp
Current Time : Apr 29 13:57:32 2011
Polling : 1024 seconds
Current Mode : unicast
NTP Status : Enabled
NTP Authenticate Status : Enabled
Last Update NTP Server : 192.168.0.88 Port: 123
Last Update Time : Mar 12 02:41:01 2013 UTC
NTP Server 192.168.0.88 version 3
NTP Server 192.168.3.21 version 3
NTP Server 192.168.4.22 version 3 key 19
NTP Authentication Key 19 md5 42V68751663T6K11P2J307210R885
Current Time : Apr 2 16:28:34 2013
Polling : 1024 seconds
Current Mode : unicast
NTP Status : Enabled
NTP Authenticate Status : Enabled
Last Update NTP Server : 192.168.5.23 Port: 0
Last Update Time : Apr 2 16:00:00 2013 UTC
NTP Server 192.168.3.20 version 3
NTP Server 192.168.3.21 version 3
NTP Server 192.168.5.23 version 3 key 19
NTP Authentication Key 45 md5 2662T75S5658RU5424180034777
Console#
– 58 –
Page 59
Section II
Command Line Interface
This section provides a detailed description of the Command Line Interface, along
with examples for all of the commands.
This section includes these chapters:
◆ "Using the Command Line Interface" on page 61
◆ "General Commands" on page 73
◆ "System Management Commands" on page 81
◆ "SNMP Commands" on page 155
◆ "Remote Monitoring Commands" on page 179
◆ "Flow Sampling Commands" on page 186
◆ "Authentication Commands" on page 191
◆ "General Security Measures" on page 250
◆ "Access Control Lists" on page 317
◆ "Interface Commands" on page 342
◆ "Link Aggregation Commands" on page 372
◆ "Power over Ethernet Commands" on page 386
◆ "Port Mirroring Commands" on page 386
◆ "Congestion Control Commands" on page 395
◆ "Loopback Detection Commands" on page 398
◆ "Address Table Commands" on page 404
– 59 –
Page 60
Section I
| Command Line Interface
◆ "Spanning Tree Commands" on page 410
◆ "VLAN Commands" on page 441
◆ "Class of Service Commands" on page 471
◆ "Quality of Service Commands" on page 483
◆ "Multicast Filtering Commands" on page 494
◆ "LLDP Commands" on page 554
◆ "Domain Name Service Commands" on page 578
◆ "DHCP Commands" on page 588
◆ "IP Interface Commands" on page 599
◆ "IP Routing Commands" on page 637
– 60 –
Page 61
2 Using the Command Line
Interface
This chapter describes how to use the Command Line Interface (CLI).
Note:
the stack.
You can only access the console interface through the Master unit in
Accessing the CLI
When accessing the management interface for the switch over a direct connection
to the server’s console port, or via a Telnet or Secure Shell connection (SSH), the
switch can be managed by entering command keywords and parameters at the
prompt. Using the switch's command-line interface (CLI) is very similar to entering
commands on a UNIX system.
Console Connection To access the switch through the console port, perform these steps:
1. At the console prompt, enter the user name and password. (The default user
names are “admin” and “guest” with corresponding passwords of “admin” and
“guest.”) When the administrator user name and password is entered, the CLI
displays the “Console#” prompt and enters privileged access mode
(i.e., Privileged Exec). But when the guest user name and password is entered,
the CLI displays the “Console>” prompt and enters normal access mode
(i.e., Normal Exec).
2. Enter the necessary commands to complete your desired tasks.
3. When finished, exit the session with the “quit” or “exit” command.
After connecting to the system through the console port, the login screen
displays:
User Access Verification
Username: admin
Password:
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
– 61 –
Page 62
Chapter 2
Console#
| Using the Command Line Interface
Accessing the CLI
Telnet Connection Telnet operates over the IP transport protocol. In this environment, your
management station and any network device you want to manage over the
network must have a valid IP address. Valid IP addresses consist of four numbers, 0
to 255, separated by periods. Each address consists of a network portion and host
portion. For example, the IP address assigned to this switch, 10.1.0.1, consists of a
network portion (10.1.0) and a host portion (1).
Note:
The IP address for this switch is obtained via DHCP by default.
To access the switch through a Telnet session, you must first set the IP
address for the Master unit, and set the default gateway if you are managing
the switch from a different IP subnet. For example,
Console(config)#interface vlan 1
Console(config-if)#ip address 10.1.0.254 255.255.255.0
Console(config-if)#exit
Console(config)#ip default-gateway 10.1.0.254
Console(config)#
If your corporate network is connected to another network outside your office
or to the Internet, you need to apply for a registered IP address. However, if
you are attached to an isolated network, then you can use any IP address that
matches the network segment to which you are attached.
After you configure the switch with an IP address, you can open a Telnet
session by performing these steps:
1. From the remote host, enter the Telnet command and the IP address or host
name of the device you want to access.
2. At the prompt, enter the user name and system password. The CLI will display
the “Vty-n#” prompt for the administrator to show that you are using privileged
access mode (i.e., Privileged Exec), or “Vty-n>” for the guest to show that you
are using normal access mode (i.e., Normal Exec), where n indicates the number
of the current Telnet session.
3. Enter the necessary commands to complete your desired tasks.
4. When finished, exit the session with the “quit” or “exit” command.
– 62 –
Page 63
Chapter 2
| Using the Command Line Interface
After entering the Telnet command, the login screen displays:
Username: admin
Password:
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Vty-0#
Entering Commands
Note:
Entering Commands
This section describes how to enter CLI commands.
Keywords and
Arguments
A CLI command is a series of keywords and arguments. Keywords identify a
command, and arguments specify configuration parameters. For example, in
the command “show interfaces status ethernet 1/5,” show interfaces and
status are keywords, ethernet is an argument that specifies the interface
type, and 1/5 specifies the unit/port.
You can enter commands as follows:
◆ To enter a simple command, enter the command keyword.
◆ To enter multiple commands, enter each command in the required order.
You can open up to eight sessions to the device via Telnet or SSH.
For example, to enable Privileged Exec command mode, and display the
startup configuration, enter the following commands. The default password
“super” is used to change from Normal Exec to Privileged Exec mode:
Minimum
Abbreviation
Console>enable
Password:
Console#show startup-config
◆ To enter commands that require parameters, enter the required
parameters after the command keyword. For example, to set a password
for the administrator, enter:
Console(config)#username admin password 0 smith
The CLI will accept a minimum number of characters that uniquely identify a
command. For example, the command “configure” can be entered as con. If an
entry is ambiguous, the system will prompt for further input.
– 63 –
Page 64
Chapter 2
| Using the Command Line Interface
Entering Commands
Command
Completion
Getting Help
on Commands
If you terminate input with a Tab key, the CLI will print the remaining characters of a
partial keyword up to the point of ambiguity. In the “logging history” example,
typing log followed by a tab will result in printing the command up to “logging.”
You can display a brief description of the help system by entering the help
command. You can also display command syntax by using the “?” character to
list keywords or parameters.
Showing Commands
If you enter a “?” at the command prompt, the system will display the first level of
keywords or command groups. You can also display a list of valid keywords for a
specific command. For example, the command “show system ?” displays a list of
possible show commands:
Console#show ?
cluster Display cluster
dns DNS information
dot1q-tunnel 802.1Q tunnel
sflow Shows the sflow information
upgrade Shows upgrade information
access-group Access groups
access-list Access lists
accounting Uses the specified accounting list
arp Information of ARP cache
authorization Enables EXEC accounting
bridge-ext Bridge extension information
cable-diagnostics Shows the information of cable diagnostics
calendar Date and time information
class-map Displays class maps
debug State of each debugging option
dns DNS information
dos-protection Shows the system dos-protection summary information
dot1q-tunnel 802.1Q tunnel
dot1x 802.1X content
history Shows history information
hosts Host information
interfaces Shows interface information
ip IP information
ipv6 IPv6 information
lacp LACP statistics
license Show license
line TTY line information
lldp LLDP
log Log records
logging Logging setting
loopback-detection Shows loopback detection information
mac MAC access list
mac-address-table Configuration of the address table
mac-vlan MAC-based VLAN information
management Shows management information
memory Memory utilization
network-access Shows the entries of the secure port.
nlm Show notification log
ntp Network Time Protocol configuration
policy-map Displays policy maps
port Port characteristics
port-channel Port channel information
power-save Shows the power saving information
– 64 –
Page 65
Chapter 2
| Using the Command Line Interface
Entering Commands
privilege Shows current privilege level
process Device process
protocol-vlan Protocol-VLAN information
public-key Public key information
qos Quality of Service
queue Priority queue information
radius-server RADIUS server information
reload Shows the reload settings
rmon Remote monitoring information
rspan Display status of the current RSPAN configuration
running-config Information on the running configuration
sflow Shows the sflow information
snmp Simple Network Management Protocol configuration and
statistics
snmp-server Displays SNMP server configuration
sntp Simple Network Time Protocol configuration
spanning-tree Spanning-tree configuration
ssh Secure shell server connections
startup-config Startup system configuration
subnet-vlan IP subnet-based VLAN information
system System information
tacacs-server TACACS server information
tech-support Technical information
time-range Time range
traffic-segmentation Traffic segmentation information
upgrade Shows upgrade information
users Information about users logged in
version System hardware and software versions
vlan Shows virtual LAN settings
voice Shows the voice VLAN information
watchdog Displays watchdog status
web-auth Shows web authentication configuration
Console#show
The command “show interfaces ?” will display the following information:
Console#show interfaces ?
brief Shows brief interface description
counters Interface counters information
history Historical sample of interface counters information
protocol-vlan Protocol-VLAN information
status Shows interface status
switchport Shows interface switchport information
transceiver Interface of transceiver information
transceiver-threshold Interface of transceiver-threshold information
Console#
Show commands which display more than one page of information (e.g.,
show running-config) pause and require you to press the [Space] bar to
continue displaying one more page, the [Enter] key to display one more line,
or the [a] key to display the rest of the information without stopping. You can
press any other key to terminate the display.
– 65 –
Page 66
Chapter 2
| Using the Command Line Interface
Entering Commands
Partial Keyword
Lookup
Negating the Effect
of Commands
Using Command
History
If you terminate a partial keyword with a question mark, alternatives that
match the initial letters are provided. (Remember not to leave a space
between the command and question mark.) For example “s?” shows all the
keywords starting with “s.”
Console#show s?
sflow snmp snmp-server sntp spanning-tree
ssh startup-config system
Console#show s
For many configuration commands you can enter the prefix keyword “no” to
cancel the effect of a command or reset the configuration to the default value.
For example, the logging command will log system messages to a host
server. To disable logging, specify the no logging command. This guide
describes the negation effect for all applicable commands.
The CLI maintains a history of commands that have been entered. You can
scroll back through the history of commands by pressing the up arrow key.
Any command displayed in the history list can be executed again, or first
modified and then executed.
Understanding
Command Modes
Using the show history command displays a longer list of recently executed
commands.
The command set is divided into Exec and Configuration classes. Exec
commands generally display information on system status or clear statistical
counters. Configuration commands, on the other hand, modify interface
parameters or enable certain switching functions. These classes are further
divided into different modes. Available commands depend on the selected
mode. You can always enter a question mark “?” at the prompt to display a list
of the commands available for the current mode. The command classes and
associated modes are displayed in the following table:
– 66 –
Page 67
Chapter 2
| Using the Command Line Interface
Entering Commands
Table 1: General Command Modes
Class Mode
Exec Normal
Privileged
Configuration
* You must be in Privileged Exec mode to access the Global configuration mode.
You must be in Global Configuration mode to access any of the other configuration modes.
Global
*
Access Control List
Class Map
DHCP
IGMP Profile
Interface
Line
Multiple Spanning Tree
Policy Map
Time Range
VLAN Database
Exec Commands When you open a new console session on the switch with the user name and
password “guest,” the system enters the Normal Exec command mode (or
guest mode), displaying the “Console>” command prompt. Only a limited
number of the commands are available in this mode. You can access all
commands only from the Privileged Exec command mode (or administrator
mode). To access Privilege Exec mode, open a new console session with the
user name and password “admin.” The system will now display the “Console#”
command prompt. You can also enter Privileged Exec mode from within
Normal Exec mode, by entering the enable command, followed by the
privileged level password “super.”
To enter Privileged Exec mode, enter the following user names and
passwords:
Username: admin
Password: [admin login password]
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Console#
Username: guest
Password: [guest login password]
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Console>enable
Password: [privileged level password]
Console#
– 67 –
Page 68
Chapter 2
| Using the Command Line Interface
Entering Commands
Configuration
Commands
Configuration commands are privileged level commands used to modify
switch settings. These commands modify the running configuration only and
are not saved when the switch is rebooted. To store the running configuration
in non-volatile storage, use the copy running-config startup-config
command.
The configuration commands are organized into different modes:
◆ Global Configuration - These commands modify the system level
configuration, and include commands such as hostname and snmpserver community.
◆ Access Control List Configuration - These commands are used for packet
filtering.
◆ Class Map Configuration - Creates a DiffServ class map for a specified
traffic type.
◆ IGMP Profile - Sets a profile group and enters IGMP filter profile
configuration mode.
◆ Interface Configuration - These commands modify the port configuration
such as speed-duplex and negotiation.
◆ Line Configuration - These commands modify the console port and Telnet
configuration, and include command such as parity and databits.
◆ Multiple Spanning Tree Configuration - These commands configure
settings for the selected multiple spanning tree instance.
◆ Policy Map Configuration - Creates a DiffServ policy map for multiple
interfaces.
◆ Time Range - Sets a time range for use by other functions, such as Access
Control Lists.
◆ VLAN Configuration - Includes the command to create VLAN groups.
To enter the Global Configuration mode, enter the command configure in
Privileged Exec mode. The system prompt will change to “Console(config)#”
which gives you access privilege to all Global Configuration commands.
Console#configure
Console(config)#
– 68 –
Page 69
Chapter 2
| Using the Command Line Interface
Entering Commands
To enter the other modes, at the configuration prompt type one of the following
commands. Use the exit or end command to return to the Privileged Exec
mode.
Table 2: Configuration Command Modes
Mode Command Prompt Page
Access Control
List
Class Map class-map Console(config-cmap) 484
Interface interface {ethernet port | port-channel id |
Line line {console | vty} Console(config-line) 111
MSTP spanning-tree mst-configuration Console(config-mstp) 416
Policy Map policy-map Console(config-pmap) 487
access-list arp
access-list ip standard
access-list ip extended
access-list ipv6 standard
access-list ipv6 extended
access-list mac
vlan id}
Console(config-arp-acl)
Console(config-std-acl)
Console(config-ext-acl)
Console(config-std-ipv6-acl)
Console(config-ext-ipv6-acl)
Console(config-mac-acl)
Console(config-if ) 343
336
318
318
324
324
331
Command Line
Processing
Time Range time-range Console(config-time-range) 146
VLAN vlan database Console(config-vlan) 442
For example, you can use the following commands to enter interface
configuration mode, and then return to Privileged Exec mode
Console(config)#interface ethernet 1/5
.
.
.
Console(config-if)#exit
Console(config)#
Commands are not case sensitive. You can abbreviate commands and parameters
as long as they contain enough letters to differentiate them from any other
currently available commands or parameters. You can use the Tab key to complete
partial commands, or enter a partial command followed by the “?” character to
display a list of possible matches. You can also use the following editing keystrokes
for command-line processing:
Table 3: Keystroke Commands
Keystroke Function
Ctrl-A Shifts cursor to start of command line.
Ctrl-B Shifts cursor to the left one character.
Ctrl-C Terminates the current task and displays the command prompt.
Ctrl-E Shifts cursor to end of command line.
Ctrl-F Shifts cursor to the right one character.
– 69 –
Page 70
Chapter 2
| Using the Command Line Interface
Entering Commands
Table 3: Keystroke Commands (Continued)
Keystroke Function
Ctrl-K Deletes all characters from the cursor to the end of the line.
Ctrl-L Repeats current command line on a new line.
Ctrl-N Enters the next command line in the history buffer.
Ctrl-P Enters the last command.
Ctrl-R Repeats current command line on a new line.
Ctrl-U Deletes from the cursor to the beginning of the line.
Ctrl-W Deletes the last word typed.
Esc-B Moves the cursor back one word.
Esc-D Deletes from the cursor to the end of the word.
Esc-F Moves the cursor forward one word.
Delete key or
backspace key
Erases a mistake when entering a command.
Showing Status
Information
There are various “show” commands which display configuration settings or
the status of specified processes. Many of these commands will not display
any information unless the switch is properly configured, and in some cases
the interface to which a command applies is up.
For example, if a static router port is configured, the corresponding show
command will not display any information unless IGMP snooping is enabled,
and the link for the static router port is up.
Console#configure
Console(config)#ip igmp snooping vlan 1 mrouter ethernet 1/11
Console(config)#end
Console#show ip igmp snooping mrouter
VLAN M'cast Router Ports Type
---- ------------------- ------Console#configure
Console(config)#ip igmp snooping
Console(config)#end
Console#show ip igmp snooping mrouter
VLAN M'cast Router Ports Type
---- ------------------- ------ 1 Eth 1/11 Static
Console#
– 70 –
Page 71
CLI Command Groups
The system commands can be broken down into the functional groups shown
below
Table 4: Command Group Index
Command Group Description Page
General Basic commands for entering privileged access mode,
System Management Display and setting of system information, basic modes of
Chapter 2
| Using the Command Line Interface
CLI Command Groups
.
restarting the system, or quitting the CLI
operation, maximum frame size, file management,
console port and telnet settings, system logs, SMTP
alerts, and the system clock
73
81
Simple Network
Management Protocol
Remote Monitoring Supports statistics, history, alarm and event groups 179
User Authentication Configures user names and passwords, command
General Security
Measures
Access Control List Provides filtering for IPv4 frames (based on address,
Interface Configures the connection parameters for all Ethernet
Link Aggregation Statically groups multiple ports into a single logical trunk;
Mirror Port Mirrors data to another port for analysis without affecting
Congestion Control Sets the input/output rate limits, traffic storm thresholds,
Activates authentication failure traps; configures
community access strings, and trap receivers
privilege levels, logon access using local or remote
authentication, management access through the web
server, Telnet server and Secure Shell; as well as port
security, IEEE 802.1X port access control, and restricted
access based on specified IP addresses
Segregates traffic for clients attached to common data
ports; and prevents unauthorized access by configuring
valid static or dynamic addresses, MAC address
authentication, filtering DHCP requests and replies, and
discarding invalid ARP responses
protocol, TCP/UDP port number or TCP control code),
IPv6 frames (based on address, DSCP traffic class, or
next header), or non-IP frames (based on MAC address or
Ethernet type)
ports, aggregated links, and VLANs
configures Link Aggregation Control Protocol for port
trunks
the data passing through or the performance of the
monitored port
and thresholds for broadcast and multicast storms which
can be used to trigger configured rate limits or to shut
down a port.
155
191
250
317
342
372
386
395
Loopback Detection Detects general loopback conditions caused by hardware
problems or faulty protocol settings
Address Table Configures the address table for filtering specified
addresses, displays current entries, clears the table, or
sets the aging time
Spanning Tree Configures Spanning Tree settings for the switch 410
398
404
– 71 –
Page 72
Chapter 2
| Using the Command Line Interface
CLI Command Groups
Table 4: Command Group Index (Continued)
Command Group Description Page
VLANs Configures VLAN settings, and defines port membership
for VLAN groups; also enables or configures private
VLANs, protocol VLANs, voice VLANs, and QinQ
tunneling
Class of Service Sets port priority for untagged frames, selects strict priority
or weighted round robin, relative weight for each priority
queue, also sets priority for DSCP
Quality of Service Configures Differentiated Services 483
441
471
Multicast Filtering Configures IGMP multicast filtering, query, profile, and
Link Layer Discovery
Protocol
Domain Name Service Configures DNS services. 578
Dynamic Host
Configuration Protocol
IP Interface Configures IP address for the switch interfaces; also
IP Routing Configures static and dynamic unicast routing 637
Debug Displays debugging information for all key functions
proxy parameters; specifies ports attached to a multicast
router; also configures multicast VLAN registration, and
IPv6 MLD snooping
Configures LLDP settings to enable information discovery
about neighbor devices
Configures DHCP client and relayfunctions 588
configures ARP parameters
These commands are not described in this manual.
Please refer to the prompt messages included in the CLI interface.
494
554
599
The access mode shown in the following tables is indicated by these
abbreviations:
ACL (Access Control List Configuration)
CM (Class Map Configuration)
GC (Global Configuration)
IC (Interface Configuration)
IPC (IGMP Profile Configuration)
LC (Line Configuration)
MST (Multiple Spanning Tree)
NE (Normal Exec)
PE (Privileged Exec)
PM (Policy Map Configuration)
VC (VLAN Database Configuration)
– 72 –
Page 73
3 General Commands
The general commands are used to control the command access mode,
configuration mode, and other basic functions.
Table 5: General Commands
Command Function Mode
prompt Customizes the CLI prompt GC
reload
(Global Confi
guration)
enable Activates privileged mode NE
quit Exits a CLI session NE, PE
show history Shows the command history buffer NE, PE
configure Activates global configuration mode PE
Restarts the system at a specified time, after a specified delay, or
at a periodic interval
GC
disable Returns to normal mode from privileged mode PE
reload Restarts the system immediately PE
show reload Displays the current reload settings, and the time at which next
scheduled reload will take place
end Returns to Privileged Exec mode any config.
exit Returns to the previous configuration mode, or exits the CLI any mode
help Shows how to use help any mode
? Shows options for command completion (context sensitive) any mode
PE
mode
prompt This command customizes the CLI prompt. Use the no form to restore the
default prompt.
Syntax
prompt string
no prompt
string - Any alphanumeric string to use for the CLI prompt.
(Maximum length: 255 characters)
Default Setting
Console
– 73 –
Page 74
Chapter 3
| General Commands
Command Mode
Global Configuration
Command Usage
This command and the hostname command can be used to set the command
line prompt as shown in the example below. Using the no form of either
command will restore the default command line prompt.
Example
Console(config)#prompt RD2
RD2(config)#
reload
(Global Configuration)
This command restarts the system at a specified time, after a specified delay,
or at a periodic interval. You can reboot the system immediately, or you can
configure the switch to reset after a specified amount of time. Use the cancel
option to remove a configured setting.
Syntax
reload {at hour minute [{month day | day month} [year]] |
in {hour hours | minute minutes | hour hours minute minutes} |
regulary
monthly
reload at - A specified time at which to reload the switch.
reload in - An interval after which to reload the switch.
hour minute [
day-of-month}] |
hour - The hour at which to reload. (Range: 0-23)
minute - The minute at which to reload. (Range: 0-59)
month - The month at which to reload. (january ... december)
day - The day of the month at which to reload. (Range: 1-31)
year - The year at which to reload. (Range: 1970-2037)
hours - The number of hours, combined with the minutes,
before the switch resets. (Range: 0-576)
period {daily
cancel [at | in |
|
weekly
day-of-week |
regulary
]}
minutes - The number of minutes, combined with the hours,
before the switch resets. (Range: 0-59)
reload
reload cancel - Cancels the specified reload option.
regulary
hour - The hour at which to reload. (Range: 0-23)
minute - The minute at which to reload. (Range: 0-59)
day-of-week - Day of the week at which to reload.
(Range: monday ... saturday)
day-of-month
31)
- A periodic interval at which to reload the switch.
- Day of the month at which to reload. (Range: 1-
– 74 –
Page 75
Chapter 3
| General Commands
Default Setting
None
Command Mode
Global Configuration
Command Usage
◆ This command resets the entire system.
◆ Any combination of reload options may be specified. If the same option is
re-specified, the previous setting will be overwritten.
◆ When the system is restarted, it will always run the Power-On Self-Test. It
will also retain all configuration information stored in non-volatile memory
by the copy running-config startup-config command (See “copy” on
page 98).
Example
This example shows how to reset the switch after 30 minutes:
Console(config)#reload in minute 30
***
*** --- Rebooting at January 1 02:10:43 2016 --***
Are you sure to reboot the system at the specified time? <y/n>
enable This command activates Privileged Exec mode. In privileged mode, additional
commands are available, and certain commands display additional
information. See “Understanding Command Modes” on page 66.
Syntax
enable [level]
level - Privilege level to log into the device.
The device has two predefined privilege levels: 0: Normal Exec,
15: Privileged Exec. Enter level 15 to access Privileged Exec mode.
Default Setting
Level 15
Command Mode
Normal Exec
Command Usage
◆ “super” is the default password required to change the command mode
from Normal Exec to Privileged Exec. (To set this password, see the
enable password command.)
– 75 –
Page 76
◆ The “#” character is appended to the end of the prompt to indicate that the
system is in privileged access mode.
Example
Console>enable
Password: [privileged level password]
Console#
Related Commands
disable (78)
enable password (192)
quit This command exits the configuration program.
Default Setting
None
Chapter 3
| General Commands
Command Mode
Normal Exec, Privileged Exec
Command Usage
The quit and exit commands can both exit the configuration program.
Example
This example shows how to quit a CLI session:
Console#quit
Press ENTER to start session
User Access Verification
Username:
show history This command shows the contents of the command history buffer.
Default Setting
None
Command Mode
Normal Exec, Privileged Exec
Command Usage
The history buffer size is fixed at 10 Execution commands and
10 Configuration commands.
– 76 –
Page 77
Chapter 3
| General Commands
Example
In this example, the show history command lists the contents of the command
history buffer:
Console#show history
Execution command history:
2 config
1 show history
Configuration command history:
4 interface vlan 1
3 exit
2 interface vlan 1
1 end
Console#
The ! command repeats commands from the Execution command history
buffer when you are in Normal Exec or Privileged Exec Mode, and commands
from the Configuration command history buffer when you are in any of the
configuration modes. In this example, the !2 command repeats the second
command in the Execution history buffer (config).
Console#!2
Console#config
Console(config)#
configure This command activates Global Configuration mode. You must enter this
mode to modify any settings on the switch. You must also enter Global
Configuration mode prior to enabling some of the other configuration modes,
such as Interface Configuration, Line Configuration, and VLAN Database
Configuration. See “Understanding Command Modes” on page 66.
Default Setting
None
Command Mode
Privileged Exec
Example
Console#configure
Console(config)#
Related Commands
end (79)
– 77 –
Page 78
Chapter 3
| General Commands
disable This command returns to Normal Exec mode from privileged mode. In normal
access mode, you can only display basic information on the switch's
configuration or Ethernet statistics. To gain access to all commands, you must
use the privileged mode. See “Understanding Command Modes” on page 66.
Default Setting
None
Command Mode
Privileged Exec
Command Usage
The “>” character is appended to the end of the prompt to indicate that the
system is in normal access mode.
Example
Console#disable
Console>
Related Commands
enable (75)
reload (Privileged Exec) This command restarts the system.
Note:
It will also retain all configuration information stored in non-volatile memory by
the copy running-config startup-config command.
Default Setting
None
Command Mode
Privileged Exec
Command Usage
This command resets the entire system.
Example
This example shows how to reset the switch:
When the system is restarted, it will always run the Power-On Self-Test.
Console#reload
System will be restarted, continue <y/n>? y
– 78 –
Page 79
Chapter 3
| General Commands
show reload This command displays the current reload settings, and the time at which next
scheduled reload will take place.
Command Mode
Privileged Exec
Example
Console#show reload
Reloading switch in time: 0 hours 29 minutes.
The switch will be rebooted at January 1 02:11:50 2015.
Remaining Time: 0 days, 0 hours, 29 minutes, 52 seconds.
Console#
end This command returns to Privileged Exec mode.
Default Setting
None
Command Mode
Global Configuration, Interface Configuration, Line Configuration, VLAN
Database Configuration, and Multiple Spanning Tree Configuration.
Example
This example shows how to return to the Privileged Exec mode from the
Interface Configuration mode:
Console(config-if)#end
Console#
exit This command returns to the previous configuration mode or exits the
configuration program.
Default Setting
None
Command Mode
Any
– 79 –
Page 80
Chapter 3
| General Commands
Example
This example shows how to return to the Privileged Exec mode from the
Global Configuration mode, and then quit the CLI session:
Console(config)#exit
Console#exit
Press ENTER to start session
User Access Verification
Username:
– 80 –
Page 81
4 System Management Commands
The system management commands are used to control system logs,
passwords, user names, management options, and display or configure a
variety of other system information.
Table 6: System Management Commands
Command Group Function
Device Designation Configures information that uniquely identifies this switch
System Status Displays system configuration, active managers, and version
Fan Control Forces fans to full speed
Frame Size Enables support for jumbo frames
File Management Manages code image or switch configuration files
information
Device Designation
Line Sets communication parameters for the serial port, including baud
rate and console time-out
Event Logging Controls logging of error messages
SMTP Alerts Configures SMTP email alerts
Time (System Clock) Sets the system clock automatically via NTP/SNTP server or
manually
Time Range Sets a time range for use by other functions, such as Access
Control Lists
Switch Clustering Configures management of multiple devices via a single IP address
This section describes commands used to configure information that uniquely
identifies the switch.
Table 7: Device Designation Commands
Command Function Mode
hostname Specifies the host name for the switch GC
snmp-server contact Sets the system contact string GC
snmp-server location Sets the system location string GC
– 81 –
Page 82
Chapter 4
| System Management Commands
System Status
hostname This command specifies or modifies the host name for this device. Use the no
form to restore the default host name.
Syntax
hostname name
no hostname
name - The name of this host. (Maximum length: 255 characters)
Default Setting
None
Command Mode
Global Configuration
Command Usage
◆ The host name specified by this command is displayed by the show
system command and on the Show > System web page.
System Status
◆ This command and the prompt command can be used to set the command
line prompt as shown in the example below. Using the no form of either
command will restore the default command line prompt.
Example
Console(config)#hostname RD#1
Console(config)#
This section describes commands used to display system information.
Table 8: System Status Commands
Command Function Mode
show access-list
tcam-utilization
show license file Shows information on the installed license file required
show memory Shows memory utilization parameters PE
show process cpu Shows CPU utilization parameters PE
show process cpu guard Shows the CPU utilization watermark and threshold NE
Shows utilization parameters for TCAM PE
PE
for the network ports
show process cpu task Shows CPU utilization per process PE
show running-config Displays the configuration data currently in use PE
show startup-config Displays the contents of the configuration file (stored in
flash memory) that is used to start up the system
– 82 –
PE
Page 83
Chapter 4
| System Management Commands
System Status
Table 8: System Status Commands (Continued)
Command Function Mode
show system Displays system information NE, PE
show access-list
tcam-utilization
show tech-support Displays a detailed list of system settings designed to
help technical support resolve configuration or
functional problems
show users Shows all active console and Telnet sessions, including
user name, idle time, and IP address of Telnet clients
show version Displays version information for the system NE, PE
show watchdog Shows if watchdog debugging is enabled PE
watchdog software Monitors key processes, and automatically reboots the
system if any of these processes are not responding
correctly
PE
NE, PE
PE
This command shows utilization parameters for TCAM (Ternary Content
Addressable Memory), including the number policy control entries in use, and
the number of free entries.
Command Mode
Privileged Exec
Command Usage
Policy control entries (PCEs) are used by various system functions which rely
on rule-based searches, including Access Control Lists (ACLs), IP Source
Guard filter rules, Quality of Service (QoS) processes, or traps.
For example, when binding an ACL to a port, each rule in an ACL will use two
PCEs; and when setting an IP Source Guard filter rule for a port, the system
will also use two PCEs.
Example
Console#show access-list tcam-utilization
Pool capability code:
AM - MAC ACL, A4 - IPv4 ACL, A6S - IPv6 Standard ACL,
A6E - IPv6 extended ACL, DM - MAC diffServ, D4 - IPv4 diffServ,
D6S - IPv6 standard diffServ, D6E - IPv6 extended diffServ,
AEM - Egress MAC ACL, AE4 - Egress IPv4 ACL,
AE6S - Egress IPv6 standard ACL, AE6E - Egress IPv6 extended ACL,
DEM - Egress MAC diffServ, DE4 - Egress IPv4 diffServ,
DE6S - Egress IPv6 standard diffServ,
DE6E - Egress IPv6 extended diffServ, W - Web authentication,
I - IP source guard, C - CPU interface, L - Link local,
MV - Mac based VLAN, PV - Protocol based VLAN, VV - Voice VLAN,
R - Routing, QINQ - QinQ, Reserved - Reserved,
ALL - All supported function,
Unit Device Pool Total Used Free Capability
---- ------ ---- ----- ----- ----- --------------------------------------- 1 0 0 128 128 0 R
1 0 1 64 0 64 A6S A6E
1 0 2 128 0 128 A4
1 0 3 128 0 128 AM
– 83 –
Page 84
Chapter 4
1 0 4 64 0 64 D6S D6E
1 0 5 128 0 128 D4 W
1 0 6 128 0 128 DM
1 0 7 128 0 128 MV PV VV
1 0 8 64 0 64 I
1 0 9 64 64 0 Reserved
1 0 10 64 64 0 C
1 0 11 64 64 0 C L
1 0 12 64 0 64 AE6S AE6E
1 0 13 128 0 128 AE4
1 0 14 128 0 128 AEM
1 0 15 64 0 64 DE6S DE6E
1 0 16 128 0 128 DE4
1 0 17 128 0 128 DEM QINQ
Console#
| System Management Commands
Table 9: show access-list tcam-utilization - display description
Field Description
Pool Capability Code Abbreviation for processes shown in the TCAM List.
Unit Stack unit identifier.
Device Memory chip used for indicated pools.
System Status
Pool Rule slice (or call group). Each slice has a fixed number of rules
that are used for the specified features.
Total The maximum number of policy control entries allocated to the
each pool.
Used The number of policy control entries used by the operating system.
Free
The number of policy control entries available for use.
Capability The processes assigned to each pool.
show license file This command shows information on the license file used to enable the
network ports.
Command Mode
Privileged Exec
Example
Console#show license file
aos-license/1.0
CPU-MAC-Address: CC-37-AB-A1-06-C0
Accept-Mode: legacy
License-Number: 0601c63c-ab32-4186-b7de-789b7bf79d66
License-Issue-Date: Fri Oct 27 06:34:18 2017
License-Valid-Start-Date: Sun Oct 1 00:00:00 2017
License-Valid-End-Date: Mon Jan 1 00:00:00 2018
License-Access-List: s/
+7N2DPboNoVfpYtNd5VASzli8yVdxD136+BV1+wfMkCdKjUZxUEypJYDi
CrYkqqjupTX13XZnOykPj/JI8rSCExCB6weC2LsvoKl3/MMxA4tY2hFhY7eEZsGeMXg/
6ttHTlVGte3JAhKd38TWrb1GwgmVWubpaxiYI5Y6S+TScnZ6VMiB2bSha349ejlk6BXgZx7Jsv+G
aoHnNYo/HZwcjZrUIvjAPmzNfd94oM1ko5H4EgIGDOwbEhwIy/bhSzLIhTKYgKXtC3nshvl1o/
l9Gw9Uv7qRVTROXasdfdfdfbvxbvsergerwert3453ferLwNwK3B75iyO5ZQMR33Vjzor3AveHue
– 84 –
Page 85
Chapter 4
| System Management Commands
System Status
/1b+Zt4OWMZlxk3wXPSxqgCNY8J3tqK+63UzwLqsEJ6GBP9q5LC9W4jsuhnzmNG1kuC0nN1rJs2/
bN74dMfql/
fYokDbaIvmpHCndJh7aqOq9wRhCMOG5UKTlo5lflX+Io+sg6PmJX7dwK8FdfrdHdWbQUsUvi6T3y
4ycwDiIiWbySjT345sdfgsdfg5445bNBPozr6l3l5hRbZqQ3WIfH1GEE9voD4GG4vbEA/
kruBOtocFDvBhXjYVe5laTkRl+vODF02eUtgYE3cGBR/
KGYcgQ+i9IRRAIWEPCKRomM69W6SsYZfdasfewcc+d430NVyf34okaUnyQrnPmqHajkLUT1BBwMF
KBuopQq1gv0Gkmuw75gUgOlGJrZ/yf1UwW/0F2MjKRTVCy4Q4Bl7IrE3DqkouscCZBKXNA==
Console#
show memory This command shows memory utilization parameters, and alarm thresholds.
Command Mode
Normal Exec, Privileged Exec
Command Usage
This command shows the amount of memory currently free for use, the
amount of memory allocated to active processes, the total amount of system
memory, and the alarm thresholds.
Example
Console#show memory
Status Bytes %
------ ---------- -- Free 111706112 41
Used 156729344 59
Total 268435456
Alarm Configuration
Rising Threshold : 95%
Falling Threshold : 90%
Console#
Related Commands
memory (176)
show process cpu This command shows the CPU utilization parameters, alarm status, and alarm
thresholds.
Command Mode
Normal Exec, Privileged Exec
Example
Console#show process cpu
CPU Utilization in the past 5 seconds : 24%
CPU Utilization in the past 60 seconds
Average Utilization : 24%
Maximum Utilization : 25%
– 85 –
Page 86
Chapter 4
Alarm Status
Current Alarm Status : Off
Last Alarm Start Time : Dec 31 00:00:19 2000
Last Alarm Duration Time : 15 seconds
Alarm Configuration
Rising Threshold : 90%
Falling Threshold : 70%
Console#
Related Commands
process cpu (177)
| System Management Commands
System Status
show process cpu
guard
This command shows the CPU utilization watermark and threshold settings.
Command Mode
Normal Exec, Privileged Exec
Example
Console#show process cpu guard
CPU Guard Configuration
Status : Disabled
High Watermark : 90%
Low Watermark : 70%
Maximum Threshold : 500 packets per second
Minimum Threshold : 50 packets per second
Trap Status : Disabled
CPU Guard Operation
Current Threshold : 500 packets per second
Console#
Table 10: show process cpu guard - display description
Field Description
CPU Guard Configuration
Status Shows if CPU Guard has been enabled.
High Watermark If the percentage of CPU usage time is higher than the high-
Low Watermark If packet flow has been stopped after exceeding the high
Maximum Threshold If the number of packets being processed by the CPU is higher than
watermark, the switch stops packet flow to the CPU (allowing it to
catch up with packets already in the buffer) until usage time falls
below the low watermark.
watermark, normal flow will be restored after usage falls beneath
the low watermark.
the maximum threshold, the switch stops packet flow to the CPU
(allowing it to catch up with packets already in the buffer) until the
number of packets being processed falls below the minimum
threshold.
– 86 –
Page 87
Chapter 4
| System Management Commands
System Status
Table 10: show process cpu guard - display description (Continued)
Field Description
Minimum Threshold If packet flow has been stopped after exceeding the maximum
threshold, normal flow will be restored after usage falls beneath the
minimum threshold.
Trap Status Shows if an alarm message will be generated when utilization
exceeds the high watermark or exceeds the maximum threshold.
CPU Guard Operation
Current Threshold Shows the configured threshold in packets per second.
Related Commands
process cpu guard (177)
show process cpu task This command shows the CPU utilization per process.
Command Mode
Privileged Exec
Example
Console#show process cpu task
Task Util (%) Avg (%) Max (%)
--------------- -------- -------- -------AMTR_ADDRESS 0.00 0.00 0.00
AMTRL3 0.00 0.00 0.00
AMTRL3_GROUP 0.00 0.00 0.00
APP_PROTOCOL_PR 0.00 0.00 0.00
AUTH_GROUP 0.00 0.00 0.00
AUTH_PROC 0.00 0.00 0.00
BGP_TD 0.00 0.00 0.00
CFGDB_TD 0.00 0.00 0.00
CFM_GROUP 0.00 0.00 0.00
CLITASK0 0.00 0.00 0.00
CORE_UTIL_PROC 0.00 0.00 0.00
DHCPSNP_GROUP 0.00 0.00 0.00
DOT1X_SUP_GROUP 0.00 0.00 0.00
DRIVER_GROUP 1.00 0.75 2.00
DRIVER_GROUP_FR 0.00 0.00 0.00
DRIVER_GROUP_TX 0.00 0.00 0.00
FS 0.00 0.00 0.00
HTTP_TD 0.00 0.00 5.00
HW_WTDOG_TD 0.00 0.00 0.00
IML_TX 0.00 0.00 0.00
IP_SERVICE_GROU 0.00 0.00 0.00
KEYGEN_TD 0.00 0.00 0.00
L2_L4_PROCESS 0.00 0.00 4.00
L2MCAST_GROUP 0.00 0.00 0.00
L2MUX_GROUP 0.00 0.00 0.00
L4_GROUP 0.00 0.00 0.00
LACP_GROUP 0.00 0.00 0.00
MSL_TD 0.00 0.00 0.00
NETACCESS_GROUP 0.00 0.00 0.00
NETACCESS_NMTR 0.00 0.25 2.00
NETCFG_GROUP 0.00 0.00 0.00
NETCFG_PROC 0.00 0.08 1.00
NIC 0.00 0.00 0.00
– 87 –
Page 88
Chapter 4
NMTRDRV 1.00 1.66 4.00
NSM_GROUP 0.00 0.00 0.00
NSM_PROC 0.00 0.00 0.00
NSM_TD 0.00 0.00 0.00
OSPF6_TD 0.00 0.00 0.00
OSPF_TD 0.00 0.00 0.00
PIM_GROUP 0.00 0.00 0.00
PIM_PROC 0.00 0.00 0.00
PIM_SM_TD 0.00 0.00 0.00
POE_PROC 0.00 0.00 0.00
RIP_TD 0.00 0.00 0.00
SNMP_GROUP 0.00 0.00 0.00
SNMP_TD 0.00 0.00 0.00
SSH_GROUP 0.00 0.00 0.00
SSH_TD 0.00 0.00 0.00
STA_GROUP 0.00 0.00 0.00
STKCTRL_GROUP 0.00 0.00 0.00
STKTPLG_GROUP 0.00 0.00 0.00
SWCTRL_GROUP 0.00 0.00 0.00
SWCTRL_TD 0.00 0.00 0.00
SWDRV_MONITOR 21.00 19.25 21.00
SYS_MGMT_PROC 0.00 0.00 0.00
SYSDRV 0.00 0.00 0.00
SYSLOG_TD 0.00 0.00 0.00
SYSMGMT_GROUP 0.00 0.00 0.00
SYSTEM 0.00 0.00 0.00
UDLD_GROUP 0.00 0.00 0.00
WTDOG_PROC 0.00 0.00 0.00
XFER_GROUP 0.00 0.00 0.00
XFER_TD 0.00 0.00 0.00
| System Management Commands
System Status
Console#
show running-config This command displays the configuration information currently in use.
Syntax
show running-config [interface interface]
interface
ethernet unit/port
unit - Unit identifier. (Range: Always 1)
port - Port number. (Range: 1-52)
port-channel channel-id (Range: 1-24)
vlan vlan-id (Range: 1-4094)
Command Mode
Privileged Exec
Command Usage
◆ Use the interface keyword to display configuration data for the specified
interface.
– 88 –
Page 89
Chapter 4
| System Management Commands
System Status
◆ Use this command in conjunction with the show startup-config command
to compare the information in running memory to the information stored in
non-volatile memory.
◆ This command displays settings for key command modes. Each mode
group is separated by “!” symbols, and includes the configuration mode
command, and corresponding commands. This command displays the
following information:
■
MAC address for
■
SNMP community strings
■
Users (names, access levels, and encrypted passwords)
■
VLAN database (VLAN ID, name and state)
■
VLAN configuration settings for each interface
■
Multiple spanning tree instances (name and interfaces)
■
IP address configured for VLANs
■
Spanning tree settings
■
Interface settings
■
Any configured settings for the console port and Telnet
◆ For security reasons, user passwords are only displayed in encrypted
format.
Example
Console#show running-config
!<stackingDB>00</stackingDB>
!<stackingMac>01_00-e0-0c-00-00-fd_03</stackingMac>
!
snmp-server community public ro
snmp-server community private rw
!
enable password 7 1b3231655cebb7a1f783eddf27d254ca
!
vlan database
VLAN 1 name DefaultVlan media ethernet
!
spanning-tree mst configuration
!
interface ethernet 1/1
no negotiation
...
interface ethernet 1/28
no negotiation
!
interface vlan 1
ip address dhcp
!
interface vlan 1
!
line console
!
line vty
!
end
!
Console#
– 89 –
Page 90
Chapter 4
| System Management Commands
System Status
Related Commands
show startup-config (90)
show startup-config This command displays the configuration file stored in non-volatile memory
that is used to start up the system.
Command Mode
Privileged Exec
Command Usage
◆ Use this command in conjunction with the show running-config
command to compare the information in running memory to the
information stored in non-volatile memory.
◆ This command displays settings for key command modes. Each mode
group is separated by “!” symbols, and includes the configuration mode
command, and corresponding commands. This command displays the
following information:
■
MAC address for
■
SNMP community strings
■
SNMP trap authentication
■
Users (names and access levels)
■
VLAN database (VLAN ID, name and state)
■
Multiple spanning tree instances (name and interfaces)
■
Interface settings and VLAN configuration settings for each interface
■
IP address for VLANs
■
Any configured settings for the console port and Telnet
Example
Refer to the example for the running configuration file.
Related Commands
show running-config (88)
show system This command displays system information.
Default Setting
None
Command Mode
Normal Exec, Privileged Exec
Example
Console#show system
System Description : SC30010
System OID String : 1.3.6.1.4.1.50868.44.101
– 90 –
Page 91
Chapter 4
| System Management Commands
System Status
System Information
System Up Time : 0 days, 23 hours, 49 minutes, and 30.37 seconds
System Name :
System Location :
System Contact :
MAC Address (Unit 1) : CC-37-AB-A1-06-C0
Web Server : Enabled
Web Server Port : 80
Web Secure Server : Enabled
Web Secure Server Port : 443
Telnet Server : Enabled
Telnet Server Port : 23
Jumbo Frame : Disabled
System Fan:
Force Fan Speed Full : Disabled
Unit 1
Fan 1: Ok
System Temperature:
Console#
Table 11: show system – display description
Parameter Description
System Description Brief description of device type.
System OID String MIB II object ID for switch’s network management subsystem.
System Up Time Length of time the management agent has been up.
System Name Name assigned to the switch system.
System Location Specifies the system location.
System Contact Administrator responsible for the system.
MAC Address MAC address assigned to this switch.
Web Server/Port Shows administrative status of web server and UDP port
Web Secure Server/Port Shows administrative status of secure web server and UDP
Telnet Server/Port Shows administrative status of Telnet server and TCP port
Jumbo Frame Shows if jumbo frames are enabled or disabled.
System Fan Shows if forced full-speed mode is enabled.
System Temperature Temperature at specified thermal detection point.
Main Power Status Displays the status of the internal power supply.
Redundant Power Status Displays the status of the redundant power supply.
number.
port number.
number.
– 91 –
Page 92
Chapter 4
| System Management Commands
System Status
show tech-support This command displays a detailed list of system settings designed to help
technical support resolve configuration or functional problems.
Command Mode
Normal Exec, Privileged Exec
Command Usage
This command generates a long list of information including detailed system
and interface settings. It is therefore advisable to direct the output to a file
using any suitable output capture function provided with your terminal
emulation program.
Example
User Access Verification
Username: admin
Password:
CLI session with the SC30010 is opened.
To end the CLI session, enter [Exit].
Vty-2#show tech-support
dir:
File Name Type Startup Modified Time Size (bytes)
------------------------------ ------- ------- ------------------- --------- Unit 1:
SC3-52T_V1.1.10.171.bix OpCode Y 2017-11-01 05:35:52 8622340
Factory_Default_Config.cfg Config N 2017-11-01 05:26:32 477
startup1.cfg Config Y 2017-11-01 05:26:35 2076
startup2.cfg Config N 2017-11-01 05:57:52 1700
Total space: 32 MB
show arp:
ARP Cache Timeout: 1200 (seconds)
IP Address MAC Address Type Interface
--------------- ----------------- --------- -----------
192.168.2.99 F0-79-59-8F-2B-FE dynamic VLAN 1
Total entry : 1
show interfaces brief:
Interface Name Status PVID Pri Speed/Duplex Type Trunk
--------- ---------------- --------- ---- --- ------------- ----------- ----Eth 1/ 1 Up 1 0 Auto-100full 1000BASE-T None
Eth 1/ 2 Dowm 1 0 Auto-100full 1000BASE-T None
Eth 1/ 3 Dowm 1 0 Auto-100full 1000BASE-T None
Eth 1/ 4 Dowm 1 0 Auto-100full 1000BASE-T None
Eth 1/ 5 Dowm 1 0 Auto-100full 1000BASE-T None
...
– 92 –
Page 93
Chapter 4
| System Management Commands
System Status
show users Shows all active console and Telnet sessions, including user name, idle time,
and IP address of Telnet client.
Default Setting
None
Command Mode
Normal Exec, Privileged Exec
Command Usage
The session used to execute this command is indicated by a “*” symbol next to
the Line (i.e., session) index number.
Example
Console#show users
User Name Accounts:
User Name Privilege Public-Key
-------------------- ---------- --------------admin 15 None
guest 0 None
Online Users:
Line Session ID User Name Idle Time (h:m:s) Remote IP Addr
--------- ---------- -------------------- ----------------- ----------------*Console 0 admin 0:00:01
Web Online Users:
Line User Name Idle Time (h:m:s) Remote IP Addr
---------- -------------------- -------------------- --------------------
Console#
show version This command displays hardware and software version information for the
system.
Command Mode
Normal Exec, Privileged Exec
Example
Console#show version
Unit 1
Serial Number : S123456
Hardware Version : R01
Number of Ports : 28
Main Power Status : Up
Role : Master
Loader Version : 0.1.1.6
Linux Kernel Version : 2.6.19
Operation Code Version : 1.2.0.4
Console#
– 93 –
Page 94
Chapter 4
| System Management Commands
Table 12: show version – display description
Parameter Description
Serial Number The serial number of the switch.
Hardware Version Hardware version of the main board.
Number of Ports Number of built-in ports.
Main Power Status Displays the status of the internal power supply.
Role Shows that this switch is operating as Master or Slave.
Loader Version Version number of loader code.
Linux Kernel Version Version number of Linux kernel.
Operation Code Version Version number of runtime code.
show watchdog This command shows if watchdog debugging is enabled.
Command Mode
Privileged Exec
System Status
Example
Console#show watchdog
Software Watchdog Information
Status : Enabled
AutoReload : Enabled
Console#
watchdog software This command monitors key processes, and automatically reboots the system
if any of these processes are not responding correctly.
Syntax
watchdog software {disable | enable}
Default Setting
Disabled
Command Mode
Privileged Exec
Example
Console#watchdog software disable
Console#
– 94 –
Page 95
Chapter 4
| System Management Commands
Fan Control
Fan Control
This section describes the command used to force fan speed. Only some of
the switches in the series support this command.
Table 13: Fan Control Commands
Command Function Mode
fan-speed force-full Forces fans to full speed GC
show system Shows if full fan speed is enabled NE, PE
fan-speed force-full This command sets all fans to full speed. Use the no form to reset the fans to
normal operating speed.
Syntax
[no] fan-speed force-full
Frame Size
Default Setting
Normal speed
Command Mode
Global Configuration
Example
Console(config)#fan-speed force-full
Console(config)#
This section describes commands used to configure the Ethernet frame size
on the switch.
Table 14: Frame Size Commands
Command Function Mode
jumbo frame Enables support for jumbo frames GC
jumbo frame This command enables support for layer 2 jumbo frames for Gigabit and
10 Gigabit Ethernet ports. Use the no form to disable it.
Syntax
[no] jumbo frame
– 95 –
Page 96
Chapter 4
| System Management Commands
File Management
Default Setting
Disabled
Command Mode
Global Configuration
Command Usage
◆ This switch provides more efficient throughput for large sequential data
transfers by supporting layer 2 jumbo frames on Gigabit and 10 Gigabit
Ethernet ports or trunks up to 10240 bytes. Compared to standard
Ethernet frames that run only up to 1.5 KB, using jumbo frames
significantly reduces the per-packet overhead required to process protocol
encapsulation fields.
◆ To use jumbo frames, both the source and destination end nodes (such as
a computer or server) must support this feature. Also, when the connection
is operating at full duplex, all switches in the network between the two end
nodes must be able to accept the extended frame size. And for half-duplex
connections, all devices in the collision domain would need to support
jumbo frames.
File Management
◆ The current setting for jumbo frames can be displayed with the show
system command.
Example
Console(config)#jumbo frame
Console(config)#
Related Commands
show system (90)
show ipv6 mtu (623)
Managing Firmware
Firmware can be uploaded and downloaded to or from an FTP/SFTP/TFTP
server. By saving runtime code to a file on an FTP/SFTP/TFTP server, that file
can later be downloaded to the switch to restore operation. The switch can
also be set to use new firmware without overwriting the previous version.
When downloading runtime code, the destination file name can be specified to
replace the current image, or the file can be first downloaded using a different
name from the current runtime code file, and then the new file set as the
startup file.
– 96 –
Page 97
Chapter 4
| System Management Commands
File Management
Saving or Restoring Configuration Settings
Configuration settings can be uploaded and downloaded to and from an FTP/
SFTP/TFTP server. The configuration file can be later downloaded to restore
switch settings.
The configuration file can be downloaded under a new file name and then set
as the startup file, or the current startup configuration file can be specified as
the destination file to directly replace it. Note that the file
“Factory_Default_Config.cfg” can be copied to the FTP/SFTP/TFTP server,
but cannot be used as the destination on the switch.
Table 15: Flash/File Commands
Command Function Mode
General Commands
boot system Specifies the file or image used to start up the system GC
copy Copies a code image or a switch configuration to or
from flash memory or an FTP/SFTP/TFTP server
delete Deletes a file or code image PE
PE
General Commands
boot system This command specifies the file or image used to start up the system.
dir Displays a list of files in flash memory PE
whichboot Displays the files booted PE
Automatic Code Upgrade Commands
upgrade opcode auto Automatically upgrades the current image when a new
version is detected on the indicated server
upgrade opcode path Specifies an FTP/SFTP/TFTP server and directory in
which the new opcode is stored
upgrade opcode reload Reloads the switch automatically after the opcode
upgrade is completed
show upgrade Shows the opcode upgrade configuration settings. PE
TFTP Configuration Commands
ip tftp retry Specifies the number of times the switch can retry
transmitting a request to a TFTP server
ip tftp timeout Specifies the time the switch can wait for a response
from a TFTP server before retransmitting a request or
timing out for the last retry
show ip tftp Displays information about TFTP settings PE
GC
GC
GC
GC
GC
Syntax
boot system {config | opcode}: filename
config* - Configuration file.
opcode* - Run-time operation code.
– 97 –
Page 98
Chapter 4
filename - Name of configuration file or code image.
* The colon (:) is required.
| System Management Commands
File Management
Default Setting
None
Command Mode
Global Configuration
Command Usage
◆ A colon (:) is required after the specified file type.
◆ If the file contains an error, it cannot be set as the default file.
Example
Console(config)#boot system config: startup
Console(config)#
Related Commands
dir (103)
whichboot (104)
copy This command moves (upload/download) a code image or configuration file
between the switch’s flash memory and an FTP/SFTP/TFTP server. When you
save the system code or configuration settings to a file on an FTP/SFTP/TFTP
server, that file can later be downloaded to the switch to restore system
operation. The success of the file transfer depends on the accessibility of the
FTP/SFTP/TFTP server and the quality of the network connection.
Syntax
copy file {file | ftp | running-config | sftp | startup-config | tftp}
copy ftp {add-to-running-config | file | https-certificate |
public-key | running-config | sftp | startup-config}
copy running-config {file | startup-config | tftp}
copy startup-config {file | running-config | tftp}
copy tftp {add-to-running-config | file | https-certificate |
public-key |
running-config | startup-config}
add-to-running-config - Keyword that adds the settings listed in
the specified file to the running configuration.
file - Keyword that allows you to copy to/from a file.
ftp - Keyword that allows you to copy to/from an FTP server.
https-certificate - Keyword that allows you to copy the HTTPS
secure site certificate.
– 98 –
Page 99
Chapter 4
public-key - Keyword that allows you to copy a SSH key from a
TFTP server. (
running-config - Keyword that allows you to copy to/from the
current running configuration.
sftp - Keyword that copies a file to or from an SFTP server.
startup-config - The configuration used for system initialization.
tftp - Keyword that allows you to copy to/from a TFTP server.
See “Secure Shell” on page 225.)
| System Management Commands
File Management
Default Setting
None
Command Mode
Privileged Exec
Command Usage
◆ The system prompts for data required to complete the copy command.
◆ The destination file name should not contain slashes (\ or /), and the
maximum length for file names is 32 characters for files on the switch or
127 characters for files on the server. (Valid characters: A-Z, a-z, 0-9, “.”, “”)
◆ The switch supports only two operation code files, but the maximum
number of user-defined configuration files is 16.
◆ You can use “Factory_Default_Config.cfg” as the source to copy from the
factory default configuration file, but you cannot use it as the destination.
◆ To replace the startup configuration, you must use startup-config as the
destination.
◆ The Boot ROM and Loader cannot be uploaded or downloaded from the
FTP/SFTP/TFTP server. You must follow the instructions in the release
notes for new firmware, or contact your distributor for help.
◆ For information on specifying an https-certificate, see “Replacing the
Default Secure-site Certificate” in the Web Management Guide. For
information on configuring the switch to
use HTTPS for a secure
connection, see the ip http secure-server command.
◆ The reload command will not be accepted during copy operations to flash
memory.
◆ When logging into an FTP server, the interface prompts for a user name
and password configured on the remote server. Note that “anonymous” is
set as the default user name.
– 99 –
Page 100
Chapter 4
| System Management Commands
File Management
◆ When logging into a remote SFTP server, the interface prompts for a user
name and password configured on the remote server. If this is a first time
connection, the system checks to see if the public key offered by the
server matches one stored locally. If not, the server’s public key will be
copied to the local system.
◆ Secure Shell FTP (SFTP) provides a method of transferring files between
two network devices over an SSH2-secured connection. SFTP functions
similar to Secure Copy (SCP), using SSH for user authentication and data
encryption.
Although the underlying premises of SFTP are similar to SCP, it requires some
additional steps to verify the protocol versions and perform security checks.
SFTP connection setup includes verification of the DSS signature, creation of
session keys, creation of client-server and server-client ciphers, SSH key
exchange, and user authentication. An SFTP channel is then opened, the SFTP
protocol version compatibility verified, and SFTP finally initialized.
◆ The reload command will not be accepted during copy operations to flash
memory.
Example
The following example shows how to download new firmware from a TFTP
server:
Console#copy tftp file
TFTP server ip address: 10.1.0.19
Choose file type:
1. config: 2. opcode: 2
Source file name: m360.bix
Destination file name: m360.bix
\Write to FLASH Programming.
-Write to FLASH finish.
Success.
Console#
The following example shows how to upload the configuration settings to a file
on the TFTP server:
Console#copy file tftp
Choose file type:
1. config: 2. opcode: 1
Source file name: startup
TFTP server ip address: 10.1.0.99
Destination file name: startup.01
TFTP completed.
Success.
Console#
– 100 –
 Loading...