

Page 1
Juniper Advanced Threat
Prevention Appliance
CLI Command Reference Guide
Release 5.0
March 2018
Page 2
Juniper Networks, Inc.
1133 Innovation Way
Sunnyvale, California 94089
USA
408-745-2000
www.juniper.net
Juniper Networks, the Juniper Networks logo, Juniper, and Junos are registered trademarks of Juniper Networks, Inc.
and/or its affiliates in the United States and other countries. All other trademarks may be property of their
respective owners.
Juniper Networks assumes no responsibility for any inaccuracies in this document. Juniper Networks reserves the
right to change, modify, transfer, or otherwise revise this publication without notice.
Juniper Advanced Threat Prevention CLI Command Reference Guide
Copyright© 2018 Juniper Networks, Inc. All rights reserved.
The information in this document is current as of the date on the title page.
YEAR 2000 NOTICE
Juniper Networks hardware and software products are Year 2000 compliant. Junos OS has no known time-related
limitations through the year 2038. However, the NTP application is known to have some difficulty in the year 2036.
END USER LICENSE AGREEMENT
The Juniper Networks product that is the subject of this technical document ation consists of (or is intended for
use with) Juniper Networks software. Use of such software is subject to the terms and conditions of the End User
License Agreement (“EULA”) posted at http://www.juniper.net/support/eula/. By downloading, installing or using
such software, you agree to the terms and conditions of that EULA.
Page 3
Draft for Review - FireEye Confidential - February 15, 2018
CONTENTS
About the Documentation
Documentation and Release Notes . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . vii
Requesting Technical Support . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . vii
Self-Help Online Tools and Resources . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . vii
Opening a Case with JTAC . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . viii
Preface
About This Guide . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1
Organization . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1
Typographical Conventions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2
Related Documentation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2
Introduction
Accessing the CLI . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3
Hardware Appliance Access via the Console . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3
Configuration Wizard Command Prompt Progressions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .4
Hardware, Software and Virtual Appliance Access via SSH . . . . . . . . . . . . . . . . . . . . . . . . . . . 6
CLI Help and Keyboard Shortcuts . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .6
CLI Modes . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7
All-in-One CLI Commands
Basic Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9
CM Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10
Core Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .10
Server Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .10
Collector Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10
Diagnosis Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .11
All-in-One CLI Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .11
capture-start . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 11
cm . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 12
collector . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .12
copy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .13
core . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .13
diagnosis . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 14
exit . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 14
gssreport . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .15
help . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 16
history . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 17
ifrestart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .17
ping . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 18
reboot . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 18
restart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 19
restore . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 20
Copyright© 2018, Juniper Networks, Inc.
Page 4

Juniper Advanced Threat Prevention Appliance
server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 20
set honeypot (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 22
set traffic-monitoring (for JATP700 Appliances only) (collector mode) . . . . . . . . . . . . . . 22
set traffic-filter (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .23
set protocols (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .23
set proxy (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .24
set (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .25
set ip interface (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 26
set (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 27
set system-alert (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 29
setupcheck . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 30
show (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 31
show (core mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .32
show (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .33
shutdown . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 34
traceroute . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 34
upgrade . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 34
updateimage . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .35
wizard . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .35
Configuration Wizard for the All-in-One Server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 36
Core/CM Server CLI Commands
Basic Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 37
CM Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 37
Core Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 38
Server Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 38
Diagnosis Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 38
CoreCM CLI Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 39
capture-start . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 39
cm . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 39
core . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 40
copy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 41
diagnosis . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 41
exit . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .42
gssreport . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .42
help . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 43
history . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 44
ifrestart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 44
ping . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 45
reboot . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 45
restart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 45
restore . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .47
set (core mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 48
server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 48
set system-alert (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 48
set (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 50
set (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .52
Copyright© 2018, Juniper Networks, Inc.
Page 5
setupcheck . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 52
show (core mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 53
show (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 55
shutdown . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 58
traceroute . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 58
upgrade . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 58
updateimage . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 59
wizard . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 59
Configuration Wizard for the CoreCM Server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 60
Mac OS X Engine CLI Commands
Basic Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 63
Core Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 63
Server Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 64
Diagnosis Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 64
Mac OS X Detection Engine CLI Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 65
capture-start . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 65
copy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 65
core . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 66
diagnosis . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 66
exit . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 67
gssreport . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 67
help . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 68
history . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 69
ifrestart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .69
ping . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 70
reboot . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 70
restart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 70
restore . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 72
server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 72
set (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 74
set (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 76
setupcheck . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 77
show (core mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 77
show (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 78
show (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 79
shutdown . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 81
traceroute . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 81
updateimage . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 81
upgrade . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 83
wizard . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 83
Configuration Wizard Command Prompt Responses . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 84
Traffic Collector CLI Commands
Basic Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 87
Collector Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 87
Diagnosis Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 88
Server Mode Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 88
CLI Command Reference Guide
Copyright© 2018, Juniper Networks, Inc.
Page 6
Juniper Advanced Threat Prevention Appliance
Traffic Collector CLI Commands . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 89
capture-start . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 89
collector . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 89
copy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 90
diagnosis . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 90
exit . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 91
gssreport . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 91
help . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 92
history . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 93
ifrestart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 93
ping . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 94
reboot . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 94
restart . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 94
restore . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 96
server . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .97
set proxy (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .97
set honeypot (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 98
set (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 99
set protocols (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 99
set (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 100
set traffic-filter (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .102
set traffic-monitoring (for JATP700 Appliances only) (collector mode) . . . . . . . . . . . . .102
setupcheck . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .103
show (collector mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 104
show (diagnosis mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 105
show (server mode) . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 106
shutdown . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 108
traceroute . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 108
wizard . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 108
Configuration Wizard Command Prompt Progressions . . . . . . . . . . . . . . . . . . . . . . . . . . . . 109
Glossary of Terms
Copyright© 2018, Juniper Networks, Inc.
Page 7
Documentation and Release Notes
To obtain the most current version of all Juniper Networks® technical documentation, see the product
documentation page on the Juniper Networks website at http://www.juniper.net/techpubs/.
If the information in the latest release notes differs from the information in the documentation, follow the product
Release Notes. Juniper Networks Books publishes books by Juniper Networks engineers and subject matter
experts. These books go beyond the technical documentation to explore the nuances of network architecture,
deployment, and administration. The current list can be viewed at http://www.juniper.net/books.
Requesting Technical Support
Technical product support is available through the Juniper Networks Technical Assistance Center (JTAC). If you are
a customer with an active J-Care or Partner Support Service support contract, or are covered under warranty, and
need post-sales technical support, you can access our tools and resources online or open a case with JTAC.
• JTAC policies—For a complete understanding of our JTAC procedures and policies, review the JTAC User Guide
located at http://www.juniper.net/us/en/local/pdf/resource-guides/7100059-en.pdf.
• Product warranties—For product warranty information, visit http://www.juniper.net/support/warranty/.
• JTAC hours of operation—The JTAC centers have resources available 24 hours a day, 7 days a week, 365 days a
year.
Self-Help Online Tools and Resources
For quick and easy problem resolution, Juniper Networks has designed an online self service portal called the
Customer Support Center (CSC) that provides you with the following features:
• Find CSC offerings: http://www.juniper.net/customers/support/.
• Search for known bugs: https://prsearch.juniper.net/.
• Find product documentation: http://www.juniper.net/documentation/.
• Find solutions and answer questions using our Knowledge Base: http://kb.juniper.net/.
• Download the latest versions of software and review release notes: http://www.juniper.net/customers/csc/
software/.
• Search technical bulletins for relevant hardware and software notifications: http://kb.juniper.net/InfoCenter/.
• Join and participate in the Juniper Networks Community Forum: http://www.juniper.net/company/
communities/.
• Open a case online in the CSC Case Management tool: http://www.juniper.net/cm/.
Copyright© 2018, Juniper Networks, Inc. i
Page 8
Juniper Advanced Threat Prevention Appliance
To verify service entitlement by product serial number, use our Serial Number Entitlement (SNE) Tool: https://
entitlementsearch.juniper.net/entitlementsearch/.
Opening a Case with JTAC
You can open a case with JTAC on the Web or by telephone.
• Use the Case Management tool in the CSC at http://www.juniper.net/cm/.
• Call 1-888-314-JTAC (1-888-314-5822 toll-free in the USA, Canada, and Mexico).
• For international or direct-dial options in countries without toll-free numbers, see http://www.juniper.net/
support/requesting-support.html
.
ii Copyright© 2018, Juniper Networks, Inc.
Page 9
This preface contains the following sections:
Preface
• About This Guide on page 1
• Organization on page 1
• Typographical Conventions on page 2
• Related Documentation on page 2
About This Guide
This guide describes the commands that make up the command-line interface (CLI) of the Juniper ATP
Appliance.
This guide is intended for system administrators responsible for deploying, operating, and maintaining the Juniper
ATP Appliance.
Organization
This guide is organized as follows:
• Chapter 1, “Introduction”—Includes an overview of CLI usage, CLI Modes and information about how to
access the Juniper ATP Appliance Command Line Interface.
• Chapter 2, “All-in-One CLI Commands”—Provides information about system commands for updating the
product boot images, setting configurations, and defining system-level settings for Collector and
Detection Engine interfaces and network deployment services.
• Chapter 3, “Core/CM Server CLI Commands”—Provides information about commands available to the
Core and Central Manager for all hardware appliance, software appliance, and virtual appliance models,
including the commands used to manage Detection Engines and Juniper ATP Appliance system
configuration.
• Chapter 4, “Mac OS X Engine CLI Commands”—Provides information about Mac Mini Mac OS X Detection
Engine-specific commands for configuration and status monitoring.
• Chapter 5, “Traffic Collector CLI Commands”—Provides information about the Juniper ATP Appliance
Traffic Collector commands available for identifying, monitoring, and configuring distributed Collector
hardware, software and virtual appliances.
• Chapter 6, “Glossary of Terms”—Provides a set Juniper ATP Appliance-specific as well as cybersecurity
industry terms and definitions.
Copyright© 2018, Juniper Networks, Inc. 1
Page 10
Juniper Advanced Threat Prevention Appliance
Typographical Conventions
This guide uses the following typographical conventions for special terms and instructions.
Table 4-1 Typographical Conventions
Convention Meaning Example
courier font Coding examples and text to be
entered at the command prompt
Enter the following command:
server set dns
Click A left-mouse button click. Click Download IVP to perform
endpoint infection verification.
Double-click A double-click of the left mouse
button.
Double-click the report name to open
in the integrated SIEM application.
Right-click A right mouse button click. Right-click on the icon to view its
properties.
< | > (text in
angle brackets;
Option for selection of required
parameter and/or value.
interfaces set stp <on | off >
items separated
by the pipe
symbols)
[ ] (text in
square
brackets)
Optional parameters and values,
with selection options separated by
the pipe symbol.
show device alarm [cpu_util | paging]
or
[ | ] (text in
square brackets,
items separated
by pipe
symbols)
Related Documentation
The following is a list of additional Juniper ATP Appliance documentation:
• Juniper ATP Appliance Release Notes— Describes the latest release of the Juniper ATP Appliance software.
• Juniper ATP Appliance Quick Start Guides— Quick Starts describe how to install and initially configure a
Juniper ATP Appliance; refer to the Quick Start for your device or model.
• Juniper ATP Appliance Operator’s Guide— The Operator’s Guide describes usage of all aspect of the Juniper
ATP Appliance All-in-One or distributed defense system.
• Juniper ATP Appliance CEF/SYSLOG Support for SIEM — This guide provides information about Juniper ATP
Appliance CEF and Syslog Logging for SIEM.
• Juniper ATP Appliance Safety and Regulatory Guide—Contains conformance and safety information for
Juniper ATP Appliances.
• Juniper ATP Appliance API Reference Guide— Provides Juniper ATP Appliance HTTP API functions and
information about usage.
2 Copyright© 2018, Juniper Networks, Inc.
Page 11
This chapter explains how to use the Juniper ATP Appliance command line interface (CLI) to configure and
CHAPTER 1
Introduction
administer a Juniper ATP Appliance.
This chapter contains the following sections:
• “Accessing the CLI” in the next section
• CLI Help and Keyboard Shortcuts on page 16
• CLI Modes on page 17
Accessing the CLI
You have the option of accessing the Juniper ATP Appliance CLI in either of two ways:
• Console
• SSH
NOTE Always use the latest version of Putty for SSH operations, if using Putty as an SSH client.
Hardware Appliance Access via the Console
To access the Juniper ATP Appliance CLI using the console port:
1. Connect your computer’s serial port to the DB-9 console port on the Juniper ATP Appliance.
2. Open a terminal program such as Console on Mac OS X, HyperTerminal on Windows, or Minicom on Linux.
3. Configure the terminal program serial communication settings as follows:
› Bits per second: 960
› Data bits: 8
› Stop bit: 1
›Parity: None
4. At the CLI prompt, enter your username and password. By default, the admin user name is admin and the
password is 1JATP234
.
Be sure to change the default password for the admin account after initial setup;
the password must be at least 8 characters in length.
5. To launch the configuration wizard, enter the command
wizard.
Copyright© 2018, Juniper Networks, Inc. 3
Page 12
Juniper Advanced Threat Prevention Appliance
# wizard
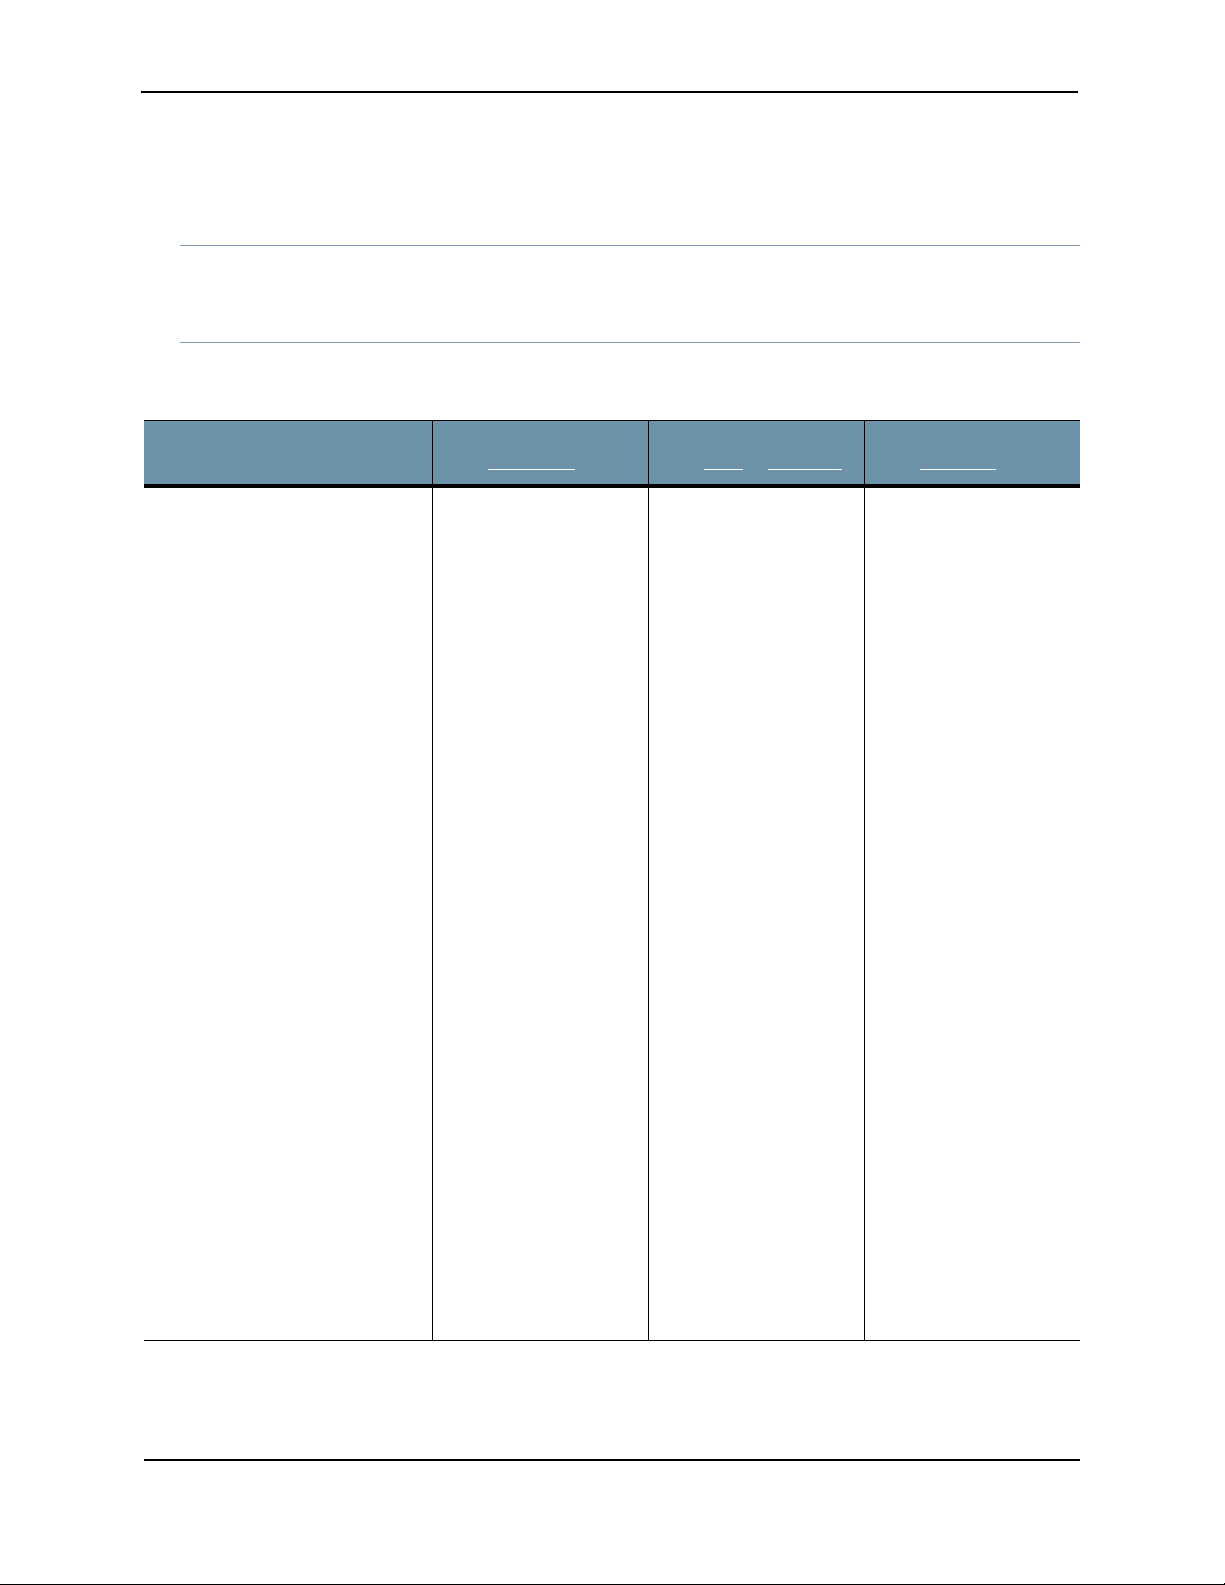
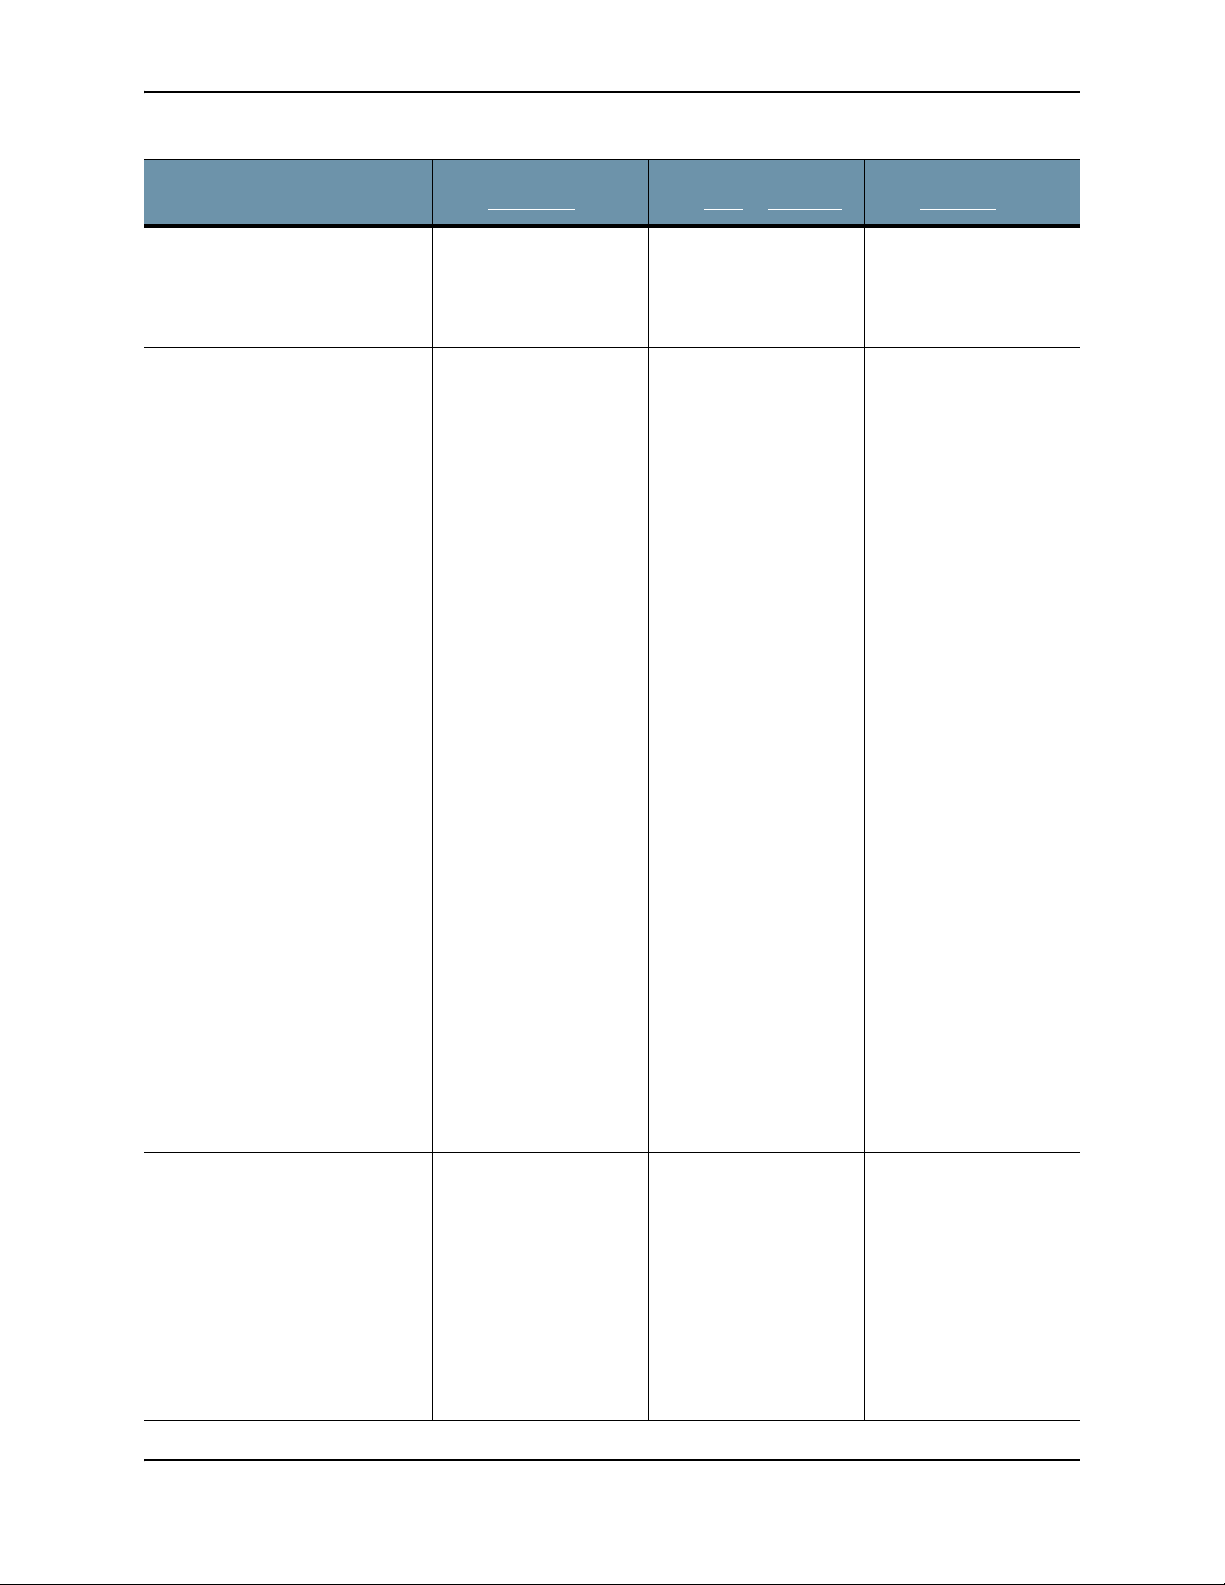
Configuration Wizard Command Prompt Progressions
NOTE Enter CTRL-C to exit the Configuration Wizard at any time. If you exit without completing the
configuration, you will be prompted again whether to run the Configuration Wizard.
You may also rerun the Configuration Wizard at any time with the CLI command wizard.
Configuration Wizard
Prompts
Use DHCP to obtain the IP
address and DNS server
address for the administrative
interface (Yes/No)?
Note: Only if your DHCP
response is no,enter the
following information when
prompted:
a. IP address
b. Netmask
c. Enter a gateway IP
address for this
management
(administrative) interface:
d. Enter primary DNS server
IP address.
e. Do you have a secondary
DNS Server (Yes/No).
Customer Response
from All-in-One
We strongly discourage
the use of DHCP
addressing because it
changes dynamically.
A static IP address is
preferred.
Recommended:
Respond with no:
a. Enter an IP address
b. Enter a netmask
using the form
255.255.255.0.
c. Enter a gateway IP
address.
d. Enter the DNS server
IP address
e. If yes, enter the IP
address of the
secondary DNS server.
Customer Response
from Core
We strongly discourage
the use of DHCP
addressing because it
changes dynamically.
A static IP address is
preferred.
Recommended:
Respond with no:
a. Enter an IP address
b. Enter a netmask
using the form
255.255.255.0.
c. Enter a gateway IP
address.
d. Enter the DNS server
IP address
e. If yes, enter the IP
address of the
secondary DNS server.
or Mac Mini
Customer Response
from Collector
We strongly discourage
the use of DHCP
addressing because it
changes dynamically.
A static IP address is
preferred.
Recommended:
Respond with no:
a. Enter an IP address
b. Enter a netmask
using the form
255.255.255.0.
c. Enter a gateway IP
address.
d. Enter the DNS server
IP address
e. If yes, enter the IP
address of the
secondary DNS server.
f. Do you want to enter the
search domains?
g. Enter the search domain
(separate multiple search
domains by space):
Restart the administrative
interface (Yes/No)?
4 Copyright© 2018, Juniper Networks, Inc.
f. Enter yes if you want
DNS lookups to use a
specific domain.
g. Enter space
domain(s) separated
by spaces; for
example: example.com
lan.com dom2.com
Enter yes to restart
with the new
configuration settings
applied.
f. Enter yes if you want
DNS lookups to use a
specific domain.
g. Enter space
domain(s) separated
by spaces; for
example: example.com
lan.com dom2.com
Enter yes to restart
with the new
configuration settings
applied.
f. Enter yes if you want
DNS lookups to use a
specific domain.
g. Enter space
domain(s) separated
by spaces; for
example: example.com
lan.com dom2.com
Enter yes to restart
with the new
configuration settings
applied.
Page 13
CLI Command Reference Guide
Configuration Wizard
Prompts
Enter a valid hostname (enter a
unique name)
[OPTIONAL]
If the system detects a
Secondary Core with an eth3
port, then the alternate CnC
exhaust option is displayed:
Use alternate-exhaust for the
analysis engine exhaust traffic
(Yes/No)?
Enter IP address for the
alternate-exhaust (eth2)
interface:
Enter netmask for the
alternate-exhaust (eth2)
interface: (example:
255.255.0.0)
Enter gateway IP Address for
the alternate-exhaust (eth2)
interface: (example:10.6.0.1)
Enter primary DNS server IP
Address for the alternateexhaust (eth2) interface:
(example: 8.8.8.8)
Do you have a secondary DNS
server for the alternate-exhaust
(eth2) interface?
Do you want to enter the search
domains for the alternateexhaust (eth2) interface?
Note: A complete network
interface restart can take more
than 60 seconds
Customer Response
from All-in-One
Type a hostname
when prompted; do
not include the
domain; for example:
juniperatp1
Refer to “Configuring
an Alternate Analysis
Engine Interface” in the
Juniper ATP Appliance
Operator’s Guide for
more information.
Enter yes to configure
an alternate eth2
interface.
Enter the IP address for
the eth2 interface.
Enter the eth2
netmask.
Enter the gateway IP
address.
Enter the primary DNS
server IP Address for
the alternate-exhaust
(eth2) interface.
Enter yes or no to
confirm or deny an
eth2 secondary DNS
server.
Enter yes or no to
indicate whether you
want to enter search
domain.
Customer Response
from Core
Type a hostname
when prompted; do
not include the
domain; for example:
juniperatp1
Refer to “Configuring
an Alternate Analysis
Engine Interface” in the
Juniper ATP Appliance
Operator’s Guide for
more information.
Enter yes to configure
an alternate eth2
interface.
Enter the IP address for
the eth2 interface.
Enter the eth2
netmask.
Enter the gateway IP
address.
Enter the primary DNS
server IP Address for
the alternate-exhaust
(eth2) interface.
Enter yes or no to
confirm or deny an
eth2 secondary DNS
server.
Enter yes or no to
indicate whether you
want to enter search
domain.
or Mac Mini
Customer Response
from Collector
Type a hostname
when prompted; do
not include the
domain; for example:
juniperatp1
[Traffic Collectors do
not send or receive
Core analysis engine
CnC network traffic, so
no eth2 interface is
needed.]
Regenerate the SSL self-signed
certificate (Yes/No)?
Enter yes to create a
new SSL certificate for
the Juniper ATP
Appliance Server Web
UI.
If you decline the selfsigned certificate by
entering no, be
prepared to install a
certificate authority
(CA) certificate.
Copyright© 2018, Juniper Networks, Inc. 5
Enter yes to create a
new SSL certificate for
the Juniper ATP
Appliance Server Web
UI.
If you decline the selfsigned certificate by
entering no, be
prepared to install a
certificate authority
(CA) certificate.
Not applicable to
Collector.
Page 14
Juniper Advanced Threat Prevention Appliance
Configuration Wizard
Prompts
Enter the following server
attributes:
Is this a Central Manager device:
Device Name: (must be unique)
Device Description
Device Key PassPhrase
NOTE: Remember this
passphrase and use it for all
distributed devices!
Customer Response
from All-in-One
Enter Yes; the system
will auto-set IP
127.0.0.1 as the All-inOne IP address.
Enter the Juniper ATP
Appliance Collector
Host Name; this
identifies the Collector
in the Web UI.
Enter a device
Description
Enter a user-defined
PassPhrase to be used
to authenticate the
Core to the Central
Manager.
Customer Response
from Core
Enter Yes; the system
will auto-set IP
127.0.0.1 as the All-inOne IP address.
Enter a Juniper ATP
Appliance Mac Mini or
Core/CM Host Name;
this identifies the Mac
OS X or Core Engine in
the Web UI.
Enter a device
Description
Enter the same
PassPhrase used to
authenticate the Core
or Mac Mini to the
Central Manager.
or Mac Mini
Customer Response
from Collector
Enter No; the system
will request that you
enter the CM IP
address now.
Enter the Juniper ATP
Appliance Collector
Host Name; this
identifies the Collector
in the Web UI.
Enter a device
Description
Enter the same
PassPhrase used to
authenticate the
Collector to the Central
Manager.
Hardware, Software and Virtual Appliance Access via SSH
To access the Juniper ATP Appliance CLI over the management network:
1. Start a terminal window session and use the ssh command to access the appliance.
For example, if the IP address of the appliance is 10.1.1.2, enter the following command:
xxxxssh [email protected]
2. When prompted, enter your password. By default, the admin user name is admin and the password is
1JATP234.
3. To launch the configuration wizard, enter the command
wizard.
# wizard
See Configuration Wizard Command Prompt Progressions for steps.
CLI Help and Keyboard Shortcuts
To display Juniper ATP Appliance CLI help, type the command help to display CLI keys and auto-completion
usage.
For context-sensitive help, alternatively, enter a “?” to display either a list of possible command completions with
summaries, or the full syntax of the current command. A subsequent repeat of this key, when a command has
been resolved, will display a detailed reference, as described below.
• Enter “?” at the prompt to display a list of the available commands in the current mode.
• Enter “?” after you type a command to display its available options and parameters.
• Enter “?” after a partially typed keyword to display command matches for auto-completions
You can enter commands in abbreviated form if you enter enough characters to uniquely identify each keyword.
For example, the show interface command can be abbreviated as:
sh in
6 Copyright© 2018, Juniper Networks, Inc.
Page 15
CLI Command Reference Guide
To identify a command’s minimum abbreviation, type a few characters then press Tab. When you have entered
enough characters, the keyword is completed.
The following table outlines the available CLI shortcuts.
Table 1-1 Keyboard Shortcuts
Action Shortcut Description
Auto-Completion Enter, Tab
or Space
Key
Recall Ctrl+P or ↑ Retrieve previous command from CLI history.
Ctrl+N or ↓ Retrieve next command from CLI history.
Ctrl+L or
Ctrl+R
Delete Ctrl+D Delete character.
Ctrl+H Delete character before cursor (Backspace).
Ctrl+K Delete all characters from cursor to end of line.
Ctrl+U or
Ctrl+W
Cursor move Ctrl+A Move cursor to start of line.
Ctrl+B Move cursor back a single character.
Ctrl+E Move cursor to end of line.
Ctrl+F Move cursor forward a single character.
Character
Transpose
Ctrl+T Transpose character at the cursor with preceding character.
Completes a partial command during typing if enough
characters are typed to uniquely identify it.
Clear the screen or Redisplay the current command line.
Delete all characters or words on line.
Interrupt output Ctrl+C Interrupt presentation of the CLI output.
Replace !! Substitute the last command line
!N Substitute the Nth command line (absolute as per 'history'
command)
!-N Substitute the command line entered N lines before
(relative)
Exit mode or
logout
exit Exit current mode or exit the CLI session.
SPECIAL CHARACTER REQUIREMENT
You must enclose non-alphabet characters in double quotes in CLI commands; for example:
Juniper ATP Appliance(server)# set passphrase “kfe$nd#$^S”
CLI Modes
The CLI commands that you can enter depend on your user privileges and the CLI command mode. User roles are
“admin” and “debugging.” The following table describes the CLI command mode.
Copyright© 2018, Juniper Networks, Inc. 7
Page 16
Juniper Advanced Threat Prevention Appliance
Note that the prompt in each mode includes the host name of the Juniper ATP Appliance.
Table 1-2 Summary of CLI Modes
Mode Description How to Exit
Basic Mode Monitor system operation and issue basic system
commands. This is the default login mode. The following
prompt is displayed:
JATP#
CM Mode Monitor system history and upgrades from the Core or
vCore in cm (Central Manager) mode.
JATP_Hostname# cm
JATP_Hostname (cm)# ?
Core
Configuration
Mode
Collector
Configuration
Mode
Diagnosis
Packet
Capture,
Monitoring,
GSS Reporting
and
Configuration
Mode
To access Core configuration mode in the Core/CM, All-inOne, and Mac Mini, enter “core” in Basic mode. The prompt
changes to indicate the mode in parentheses:
JATP_Hostname# core
JATP_Hostname (core)# ?
Configure the Juniper ATP Appliance Collector (includes all
commands). To access Collector configuration mode,
enter “collector” in Basic mode. The prompt changes to
indicate the mode in parentheses:
JATP_Hostname# collector
JATP_Hostname (collector)# ?
Check Initial Setup, Diagnose, Monitor, Set GSS, and
Configure the Juniper ATP Appliance (includes all
commands). To access Diagnosis mode, enter
“diagnosis” in Basic mode. The prompt changes to
indicate the mode in parentheses:
JATP_Hostname# diagnosis
JATP_Hostname (diagnosis)# ?
Enter exit to log
out of the CLI.
Enter exit to
leave cm mode.
Enter exit to
leave server
mode.
Enter exit to
leave server
mode.
Enter exit to
leave diagnosis
mode.
Server
Configuration
Mode
Wizard
Configuration
Mode
8 Copyright© 2018, Juniper Networks, Inc.
Set up and monitor the system (includes all Basic
commands plus server-specific commands). To access
Server configuration mode, enter “server” in Basic mode.
The prompt changes to indicate the mode in parentheses:
JATP-Hostname# server
JATP-Hostname (server)# ?
Configure the system during installation and setup the
management network and connected Juniper ATP
Appliance components. To access wizard configuration
mode, enter “wizard” in Basic mode. The prompt changes
to indicate the mode in parentheses:
JATP-Hostname# wizard
JATP-Hostname (wizard)# ?
Enter exit to
leave server
mode.
Enter exit to
leave wizard
mode.
Page 17
This chapter describes the administration commands for a Juniper ATP Appliance All-in-One server appliance,
CHAPTER 2
All-in-One CLI Commands
software appliance or virtual appliance.
These commands are used to configure the Juniper ATP Appliance All-in-One appliance, manage configurations,
and set system-level settings for interfaces, network services, and SIEM integration.
NOTE You must enclose non-alphabet characters in double quotes in CLI commands.
Basic Mode Commands
Use general system commands to configure the appliance, view appliance history, enter other CLI modes, obtain
help with CLI syntax, and to exit the CLI session.
The general commands are:
• cm on page 12
• core on page 13
• collector on page 12
• diagnosis on page 14
• exit on page 14
• help on page 16
• history on page 17
• server on page 20
• wizard on page 35
Refer to the sections in this guide to review CM Mode, Collector Mode, Core Mode, Diagnosis Mode, Server Mode
and Wizard mode commands per device-- All-in-One, CoreCM, Traffic Collector and Mac OS X Detection Engine
on a Mac Mini.
Copyright© 2018, Juniper Networks, Inc. 9
Page 18
Juniper Advanced Threat Prevention Appliance
CM Commands
• exit on page 14
• help on page 16
• history on page 17
• upgrade on page 34
Core Mode Commands
• exit on page 14
• help on page 16
• history on page 17
• show (core mode) on page 32
• updateimage on page 35
Server Mode Commands
• exit on page 14
• help on page 16
• history on page 17
• ifrestart on page 17
• ping on page 18
• reboot on page 18
• restart on page 19
• restore on page 20
• set ip interface (server mode) on page 26
• set system-alert (server mode) on page 29
• set (server mode) on page 27
• shutdown on page 34
• shutdown on page 34
• traceroute on page 34
Collector Mode Commands
• exit on page 14
• help on page 16
• history on page 17
• set honeypot (collector mode) on page 22
• set traffic-monitoring (for JATP700 Appliances only) (collector mode) on page 22
• set traffic-filter (collector mode) on page 23
• set protocols (collector mode) on page 23
• set proxy (collector mode) on page 24
• set traffic-filter (collector mode) on page 23
• show (collector mode) on page 31 [show proxy inside or show proxy outside]
10 Copyright© 2018, Juniper Networks, Inc.
Page 19
Diagnosis Mode Commands
• capture-start on page 11
• copy on page 13
• exit on page 14
• gssreport on page 15
• help on page 16
• history on page 17
• set (diagnosis mode) on page 25
• setupcheck on page 30
• show (diagnosis mode) on page 33
All-in-One CLI Commands
capture-start
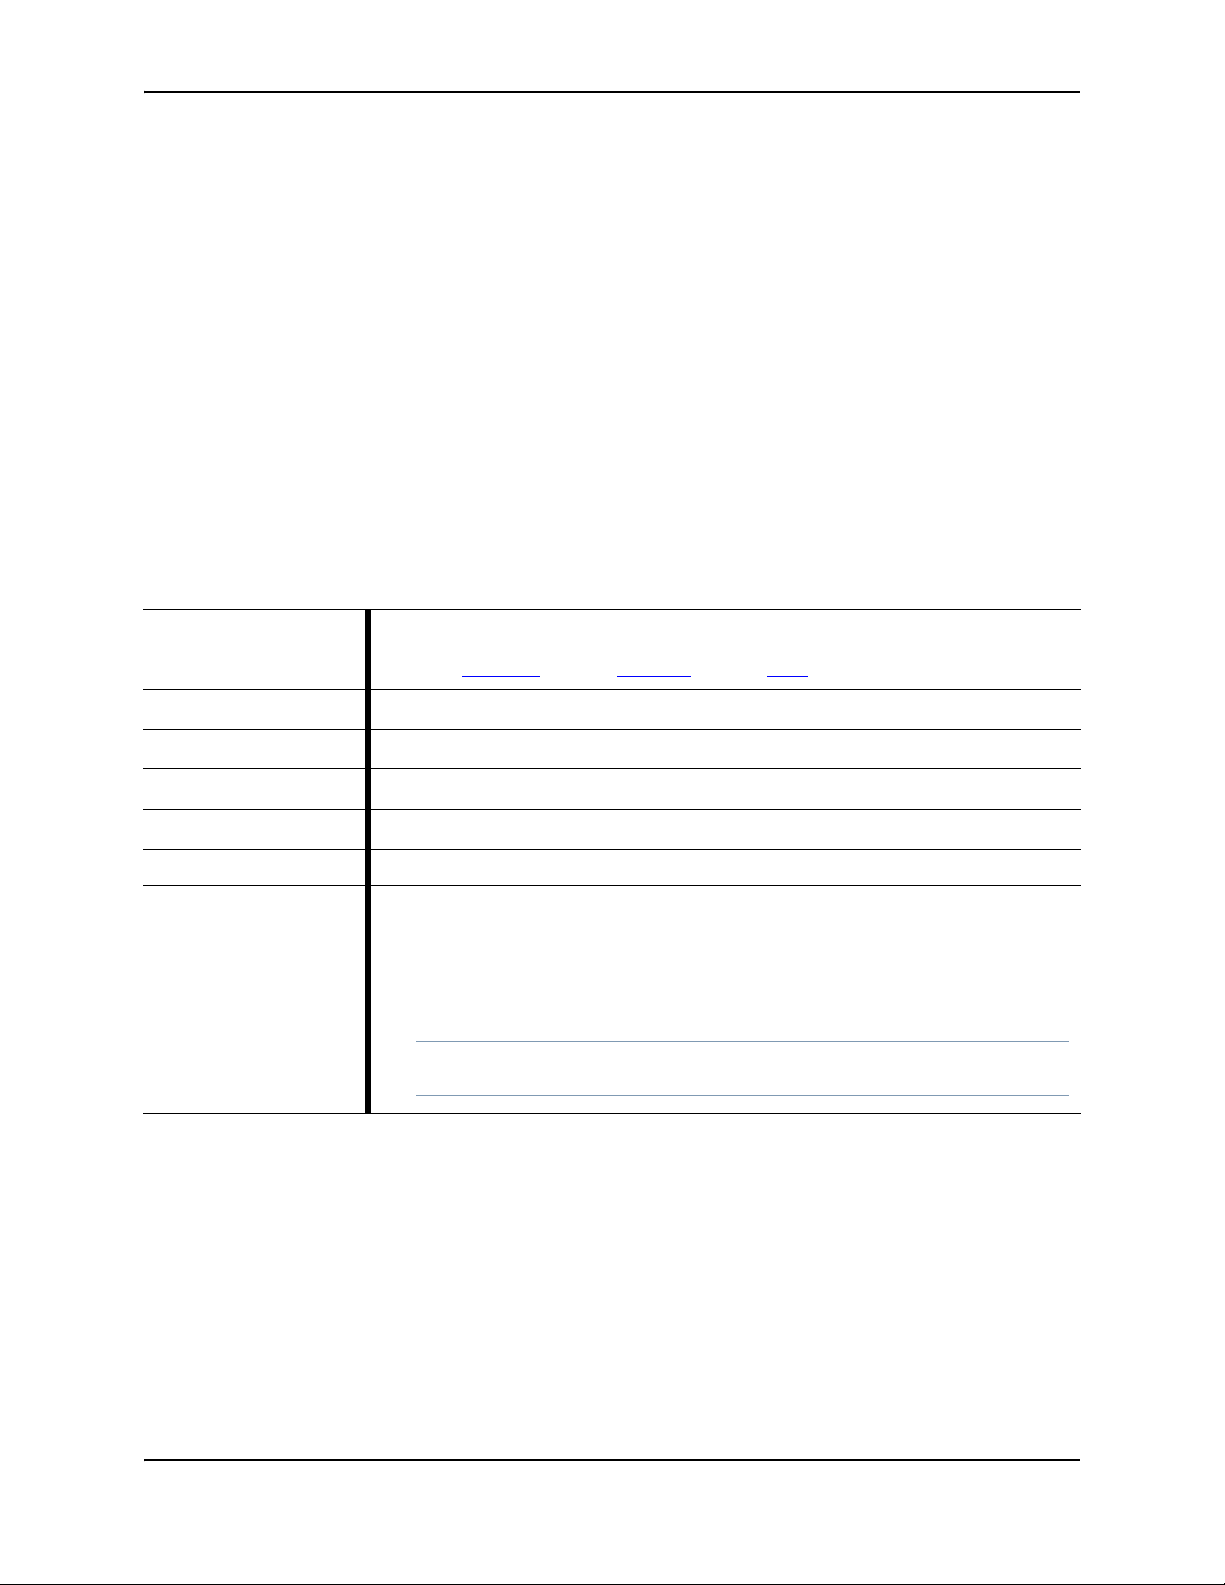
Table 2-1 capture-start
Starts packet capture as a means for diagnosing and debugging network traffic and
Description
obtaining stats.
See Also: diagnosis
CLI Command Reference Guide
[mode]; collector [mode]; copy
Product(s) CLI
Mode(s)
Syntax
Parameters
Sub-Commands None
All-in-One | Collector
Diagnosis
capture-start
<IP address> <interface_name>
The following example starts a packet capture process on interface eth1 for a
Traffic Collector with IP address 8.8.8.8:
hostname # diagnosis
Example
hostname (diagnosis)# capture-start 8.8.8.8 eth1
NOTE Note: Address 8.8.8.8 need not be a Juniper ATP Appliance. It is just a
host that the capture filters on.
Copyright© 2018, Juniper Networks, Inc. 11
Page 20
Juniper Advanced Threat Prevention Appliance
cm
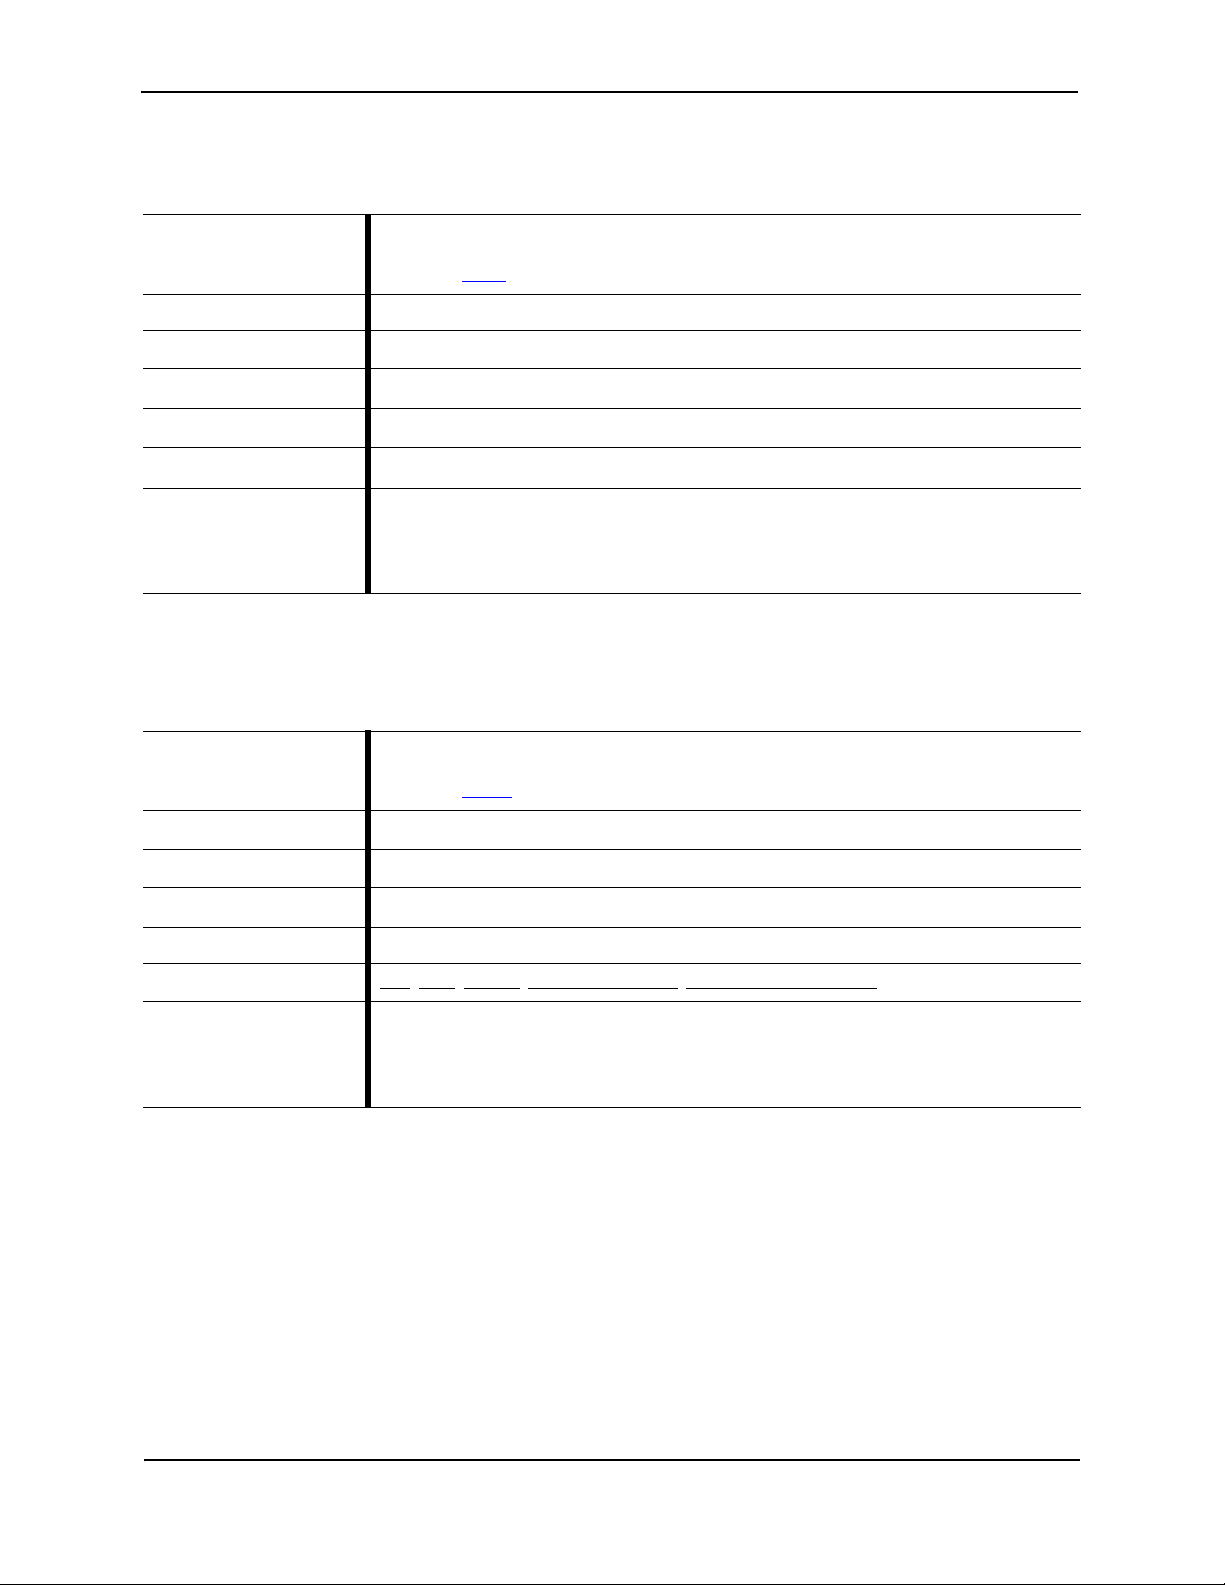
Table 2-2 cm
Enters cm (Central Manager) mode.
Description
See Also: basic
Product(s) CLI All-in-One | Core
Mode(s) Basic
[mode];
Syntax
Parameters
Sub-Commands
Example
cm
None
exit | help | history | upgrade
The following command example enters cm configuration mode:
hostname # cm
hostname (cm)#
collector
Table 2-3 collector
Enters the Collector configuration mode.
Description
See Also: server
Product(s) CLI
Mode(s) Basic
Syntax
Parameters None
All-in-One | Collector
collector
[mode]
Sub-Commands exit
Example
; help; history; set (server mode); show (collector mode)
The following example enters collector configuration mode:
hostname # collector
hostname (collector)# ?
12 Copyright© 2018, Juniper Networks, Inc.
Page 21
copy
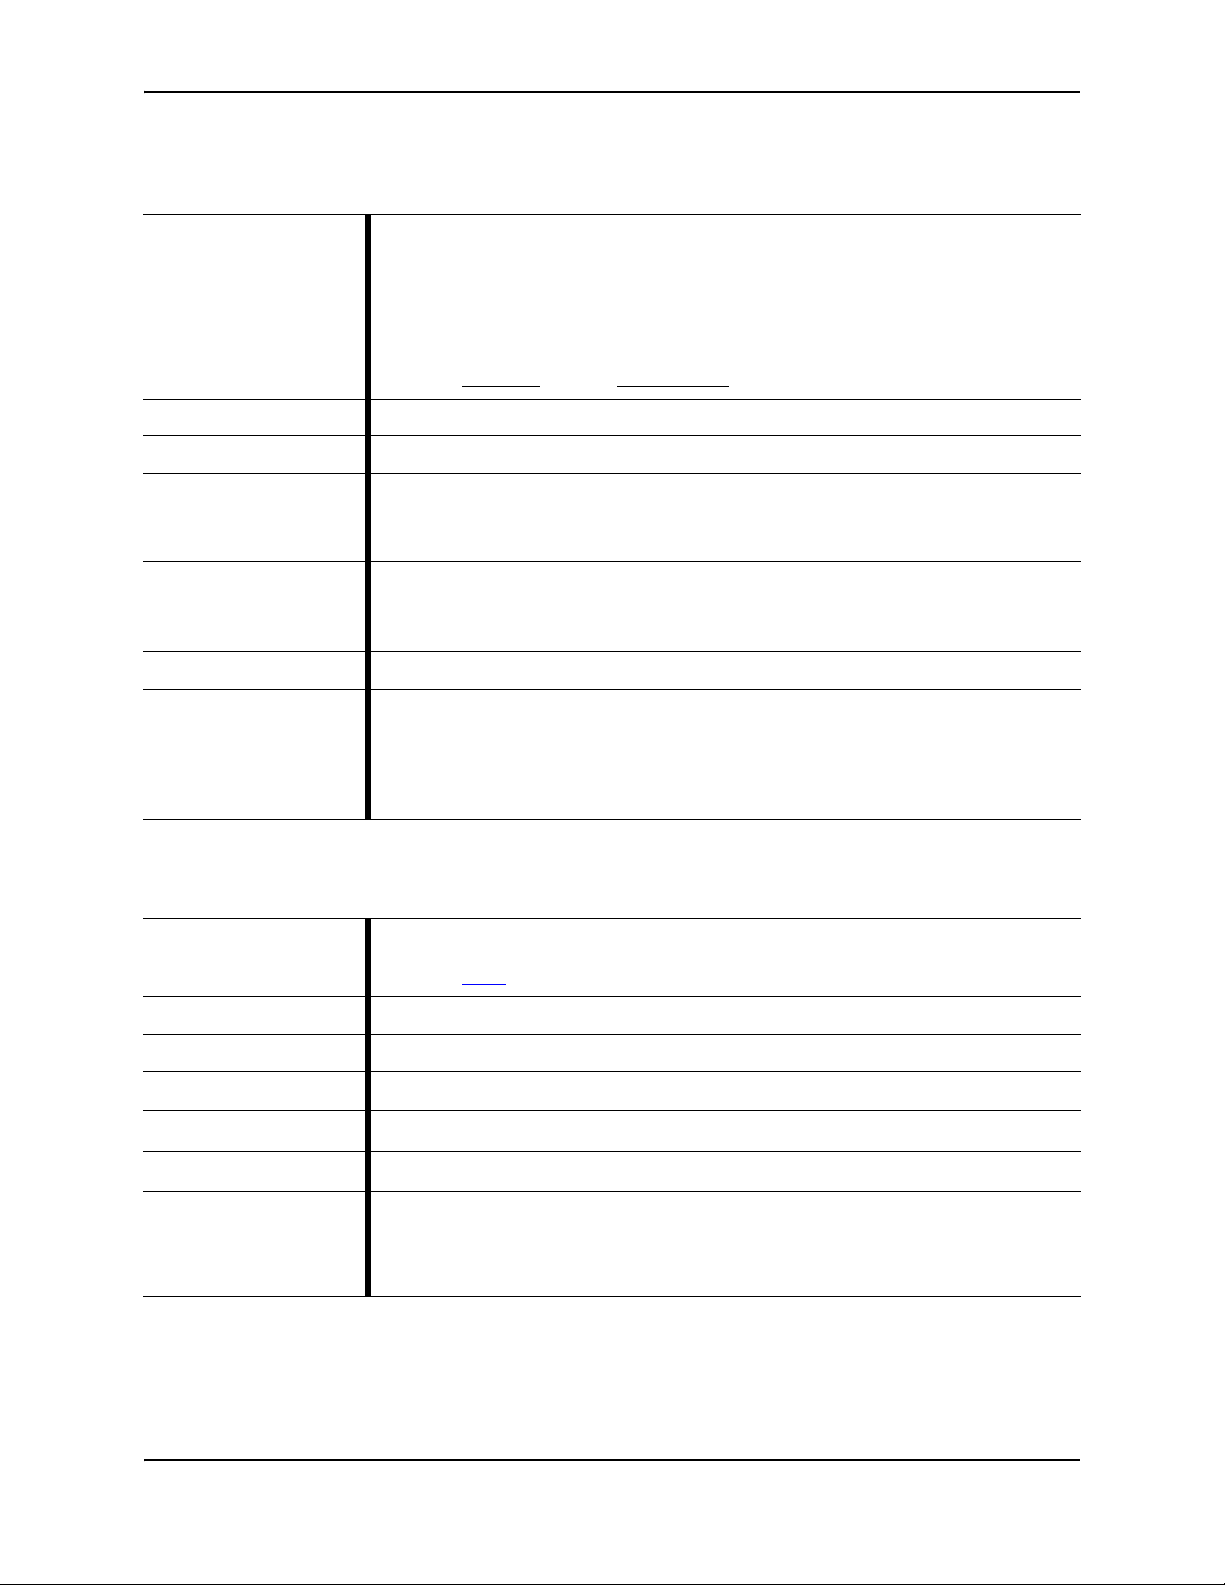
Table 2-4 copy
Description
CLI Command Reference Guide
Uses Secure Copy (SCP) to copy and transfer packet capture or traceback (crash)
data to a remote location, providing the same authentication and level of security
as an SSH transfer.
The copy traceback command, upon Customer Support's request, copies the
traceback files out of the box to a remote location.
See Also: diagnosis
Product(s) CLI All-in-One | Collector | Core-CM | Mac OSX Engine
Mode(s) Diagnosis
[mode]; capture-start
copy capture <scp source_file_name
Syntax
username@destination_host:destination_folder> | traceback
{<tab> | ALL} <string URI as user@hostname:path
copy capture <scp remote filename_location>
Parameters
Sub-Commands None
Example
core
Table 2-5 core
Description
copy traceback <ALL | filename>
copy traceback <tab> [tab displays all available crash filenames]
The following example copies the file "Eth1.txt" from the local host to a remote
host:
hostname (diagnosis)# copy capture Eth1.txt
[email protected]:/some/remote/directory
Enters core mode.
See Also: basic
[mode];
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Basic
Syntax
Parameters
Sub-Commands
Example
core
None
exit, help, history, show, updateimage
The following command example enters core configuration mode:
hostname # core
hostname (core)#
Copyright© 2018, Juniper Networks, Inc. 13
Page 22
Juniper Advanced Threat Prevention Appliance
diagnosis
Table 2-6 diagnosis
Enters the Diagnosis configuration and status check mode.
Description
See Also: collector [mode], server [mode]
Product(s) CLI All-in-One | Collector | Mac OS X Detection Engine
Mode(s) Basic
Syntax
Parameters None
Sub-Commands
diagnosis
capture-start; copy; exit; gssreport; help; history; set
(server mode); setupcheck; show (diagnosis mode); shutdown
The following example enters diagnosis configuration and status check mode:
Example
exit
Table 2-7 exit
Description Ends the CLI session.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Core | Collector | Diagnosis | Server
Syntax
Parameters None
Example
hostname # diagnosis
hostname (diagnosis)# ?
exit
The following example ends a command mode or CLI session.
JATP# (diagnosis) exit
JATP#
JATP (core) exit
JATP# exit
14 Copyright© 2018, Juniper Networks, Inc.
Page 23
gssreport
Table 2-8 gssreport
Use the gssreport command to submit reports to Juniper Global Security Services
Description
Product(s) CLI All-in-One | Collector | Mac OS X Detection Engine
Mode(s) diagnosis
(GSS), and to display the status of the current GSS report.
See Also: gssreport
; diagnosis [mode]
CLI Command Reference Guide
Syntax
Parameters
Sub-Commands None
gssreport status | submit
status - displays the status of the current GSS report.
submit - submits a report to Juniper ATP Appliance GSS.
The following examples display the status of a GSS report submission:
hostname # diagnosis
hostname (diagnosis)# gssreport submit
Successfully started GSS report
Example
hostname (diagnosis)# gssreport status
GSS is currently enabled
Last 5-minute GSS report at 2015-07-28 10:34:24.414322:
successfully submitted
Last hourly GSS report at 2015-07-28 10:34:24.468259:
successfully submitted
Last daily GSS report at 2015-07-28 10:34:28.225512:
successfully submitted
Copyright© 2018, Juniper Networks, Inc. 15
Page 24
Juniper Advanced Threat Prevention Appliance
help
Table 2-9 help
Description Displays information about the CLI help system.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Core | Collector | Diagnosis | Server
Syntax
Parameters
Example
help
None
The following example shows some of the output of the help command.
CONTEXT SENSITIVE HELP
[?] - Display context sensitive help. This is either a list of
possible command completions with summaries, or the full syntax
of the current command. A subsequent repeat of this key, when a
command has been resolved, will display a detailed reference.
AUTO-COMPLETION
The following keys both perform auto-completion for the current
command line. If the command prefix is not unique then the bell
will ring and a subsequent repeat of the key will display
possible completions.
[enter] - Auto-completes, syntax-checks then executes a command.
If there is a syntax error then offending part of the command
line will be highlighted and explained.
[tab] - Auto-completes
[space] - Auto-completes, or if the command is already resolved
inserts a space.
If “<cr>” is shown, that means that what you have entered so
far is a complete command, and you may press Enter (carriage
return) to execute it.
Use ? to learn command parameters and option:
JATP (server)# show f?
firewall Show the firewall configuration settings
interface
JATP (server)# show firewall?
all Show the current iptables settings
whitelist Show the iptables whitelist settings
show firewall whitelist?
<cr>
show firewall whitelist
16 Copyright© 2018, Juniper Networks, Inc.
Page 25
CLI Command Reference Guide
eth0 Restarts the management network administra
interface.
eth1 Restarts the monitoring network interface.
history
Table 2-10 history
Description Displays the current CLI session command line history.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Core | Collector | Diagnosis | Server
Syntax
Parameters None
Example
history
The following examples returns command line history for the current CLI session.
JATP# (core) history
ifrestart
Table 2-11 ifrestart
Description Restarts the interface driver and services using the interface.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
ifrestart eth0 | eth1
The following example restarts the eth0 interface for the management network.
<FireEye_name># ifrestart eth0
Copyright© 2018, Juniper Networks, Inc. 17
Page 26
Juniper Advanced Threat Prevention Appliance
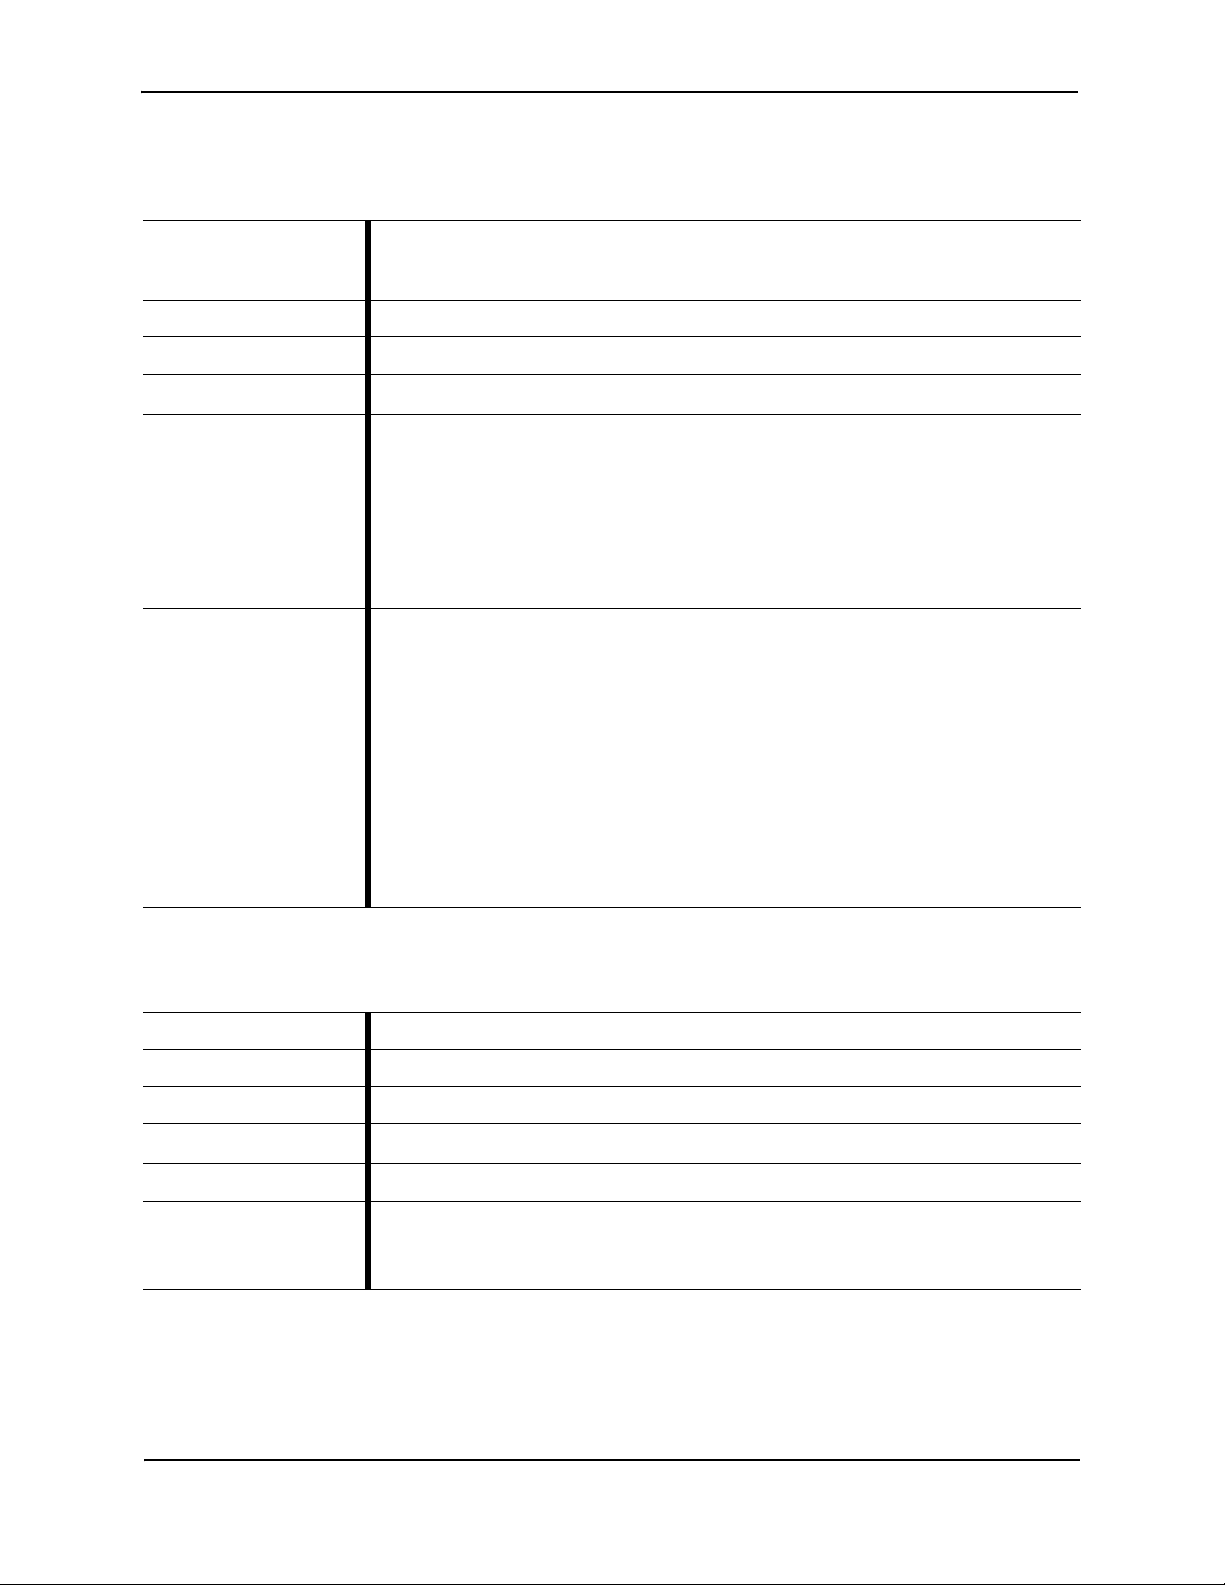
-c count Number of echo requests to send. By default, pings ar
continuously until you press Ctrl+C.
-h hops Number of next hops between pings (default is 1).
string IP address, hostname or interface name used to ping
device address.
ping
Table 2-12 ping
Sends ICMP (Internet Control Message Protocol) echo request packets to a
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
specified host name or IP address to verify that the destination is reachable over
the network.
Syntax
Parameters
Example
reboot
ping [-c count] [-h hops] [string]
The following example sends three echo requests to the device with the IP Address
10.10.10.1
<FireEye_name># ping -c 3 10.10.10.1
PING 10.10.10.1 (10.10.10.1) 56(84) bytes of data.
64 bytes from 10.10.10.1: icmp_req=1 ttl=64 time=0.314 ms
64 bytes from 10.10.10.1: icmp_req=2 ttl=64 time=0.277 ms
64 bytes from v: icmp_req=3 ttl=64 time=0.274 ms
--- 10.10.10.1 ping statistics --3 packets transmitted, 3 received, 0% packet loss, time
bbbb1999ms
rtt min/avg/max/mdev = 0.274/0.288/0.314/0.022 ms
Table 2-13 reboot
Description Reboots the Juniper ATP Appliance.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
reboot
None
The following example reboots the system.
hostname# reboot
18 Copyright© 2018, Juniper Networks, Inc.
Page 27
CLI Command Reference Guide
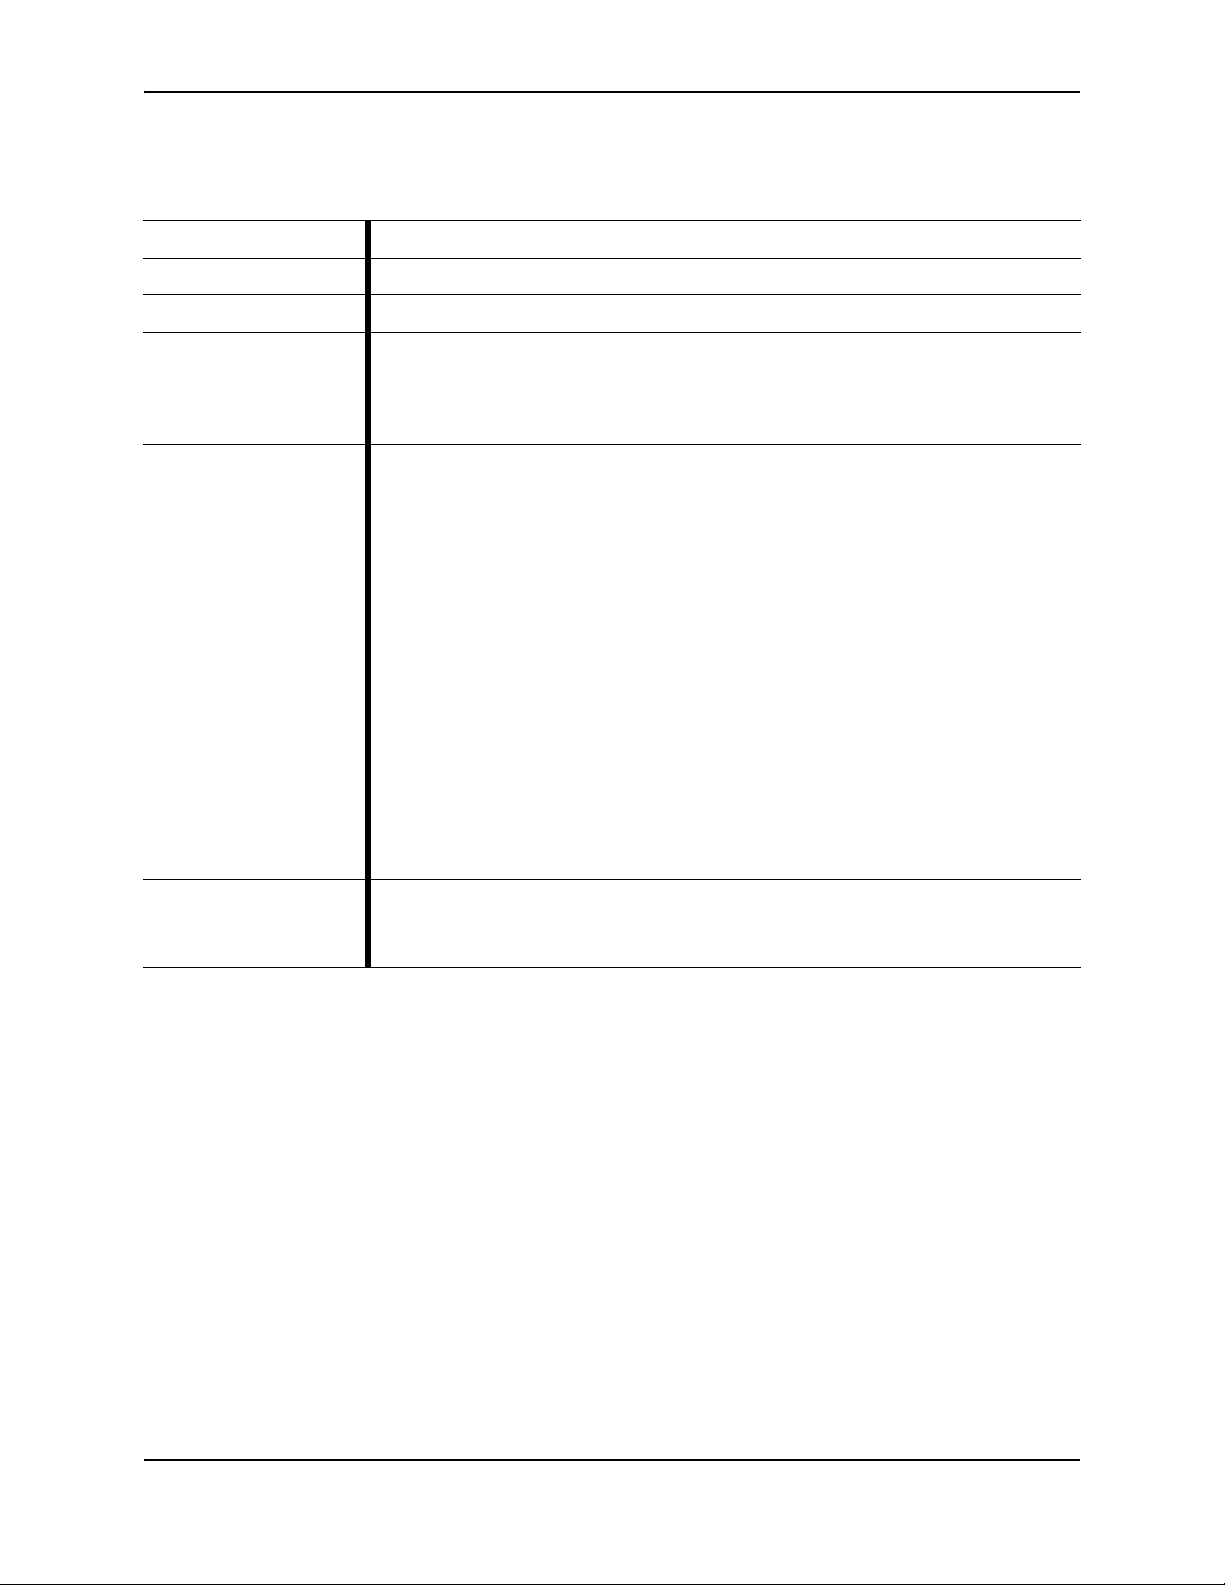
all
Restarts all Juniper ATP Appliance services.
behaviorengine Restarts the Behavioral Analysis Engine.
cm Restarts the Central Manager Web UI service.
collector
Restarts the Collector service.
core Restarts the Core Detection Engine.
correlationengine Restarts the Correlation Engine.
database Restarts the Database.
ntpserver Restarts the NTP server.
sshserver Restarts the SSH server.
staticengine Restarts the Static Analysis Engine.
webserver Restarts the web server.
restart
Table 2-14 restart
Description Restarts Juniper ATP Appliance services.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
restart [all | behaviorengine | cm | collector | core |
Syntax
correlationengine | database | ntpserver | sshserver |
staticengine | webserver]
Parameters
The following example restarts the Central manager service.
Example
JATP# restart cm
Copyright© 2018, Juniper Networks, Inc. 19
Page 28
Juniper Advanced Threat Prevention Appliance
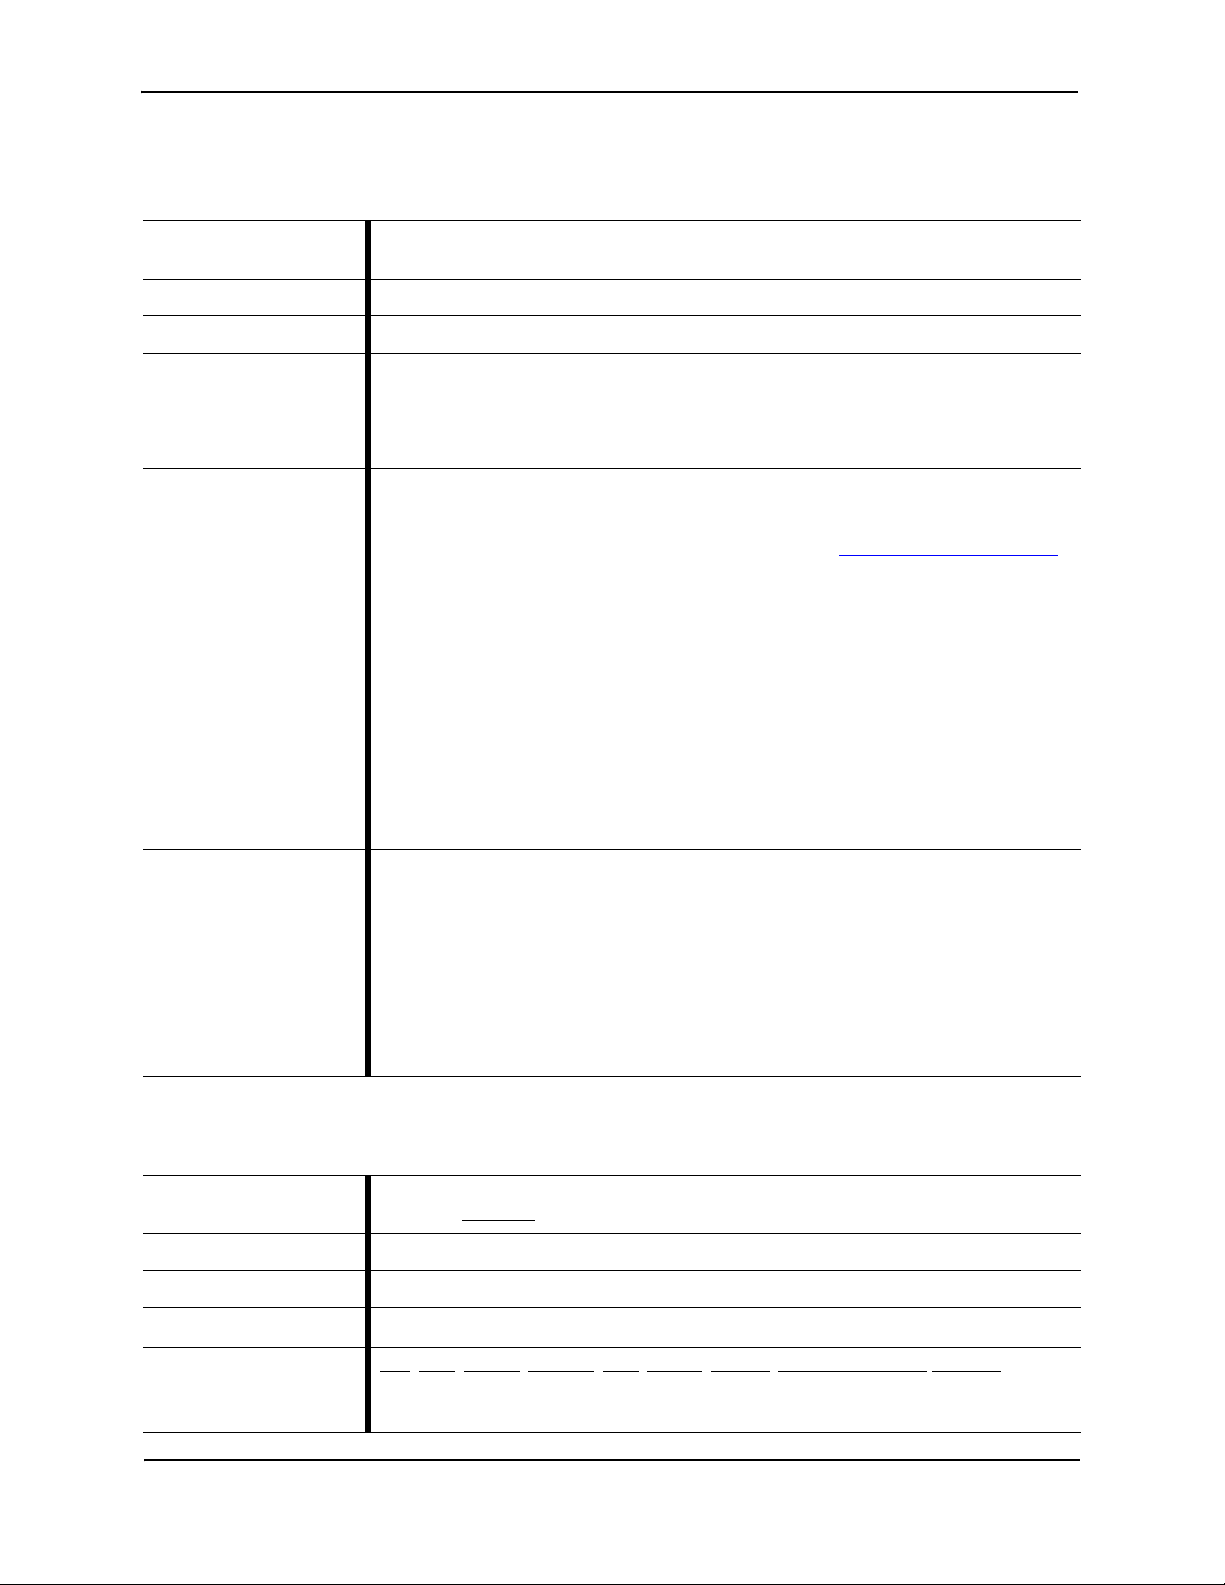
support Restores the default support password setting
remote login (set during initial installation per l
See also (server)# set (server mode) support
firewall {backup | default} Restores the firewall settings from either the pr
backup, or from the default factory settings.
hostname Restores the system’s hostname to the factory
hostname.
network Restores the IP address and DNS settings to th
factory default settings.
WARNING: This command option removes the
IP address and DNS settings, and reloads the d
values for these settings.
restore
Table 2-15 restore
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Restores the system configuration to the factory default settings.
This will only reset the password to default temporarily.
restore [support | firewall {backup | default} | hostname
Syntax
Parameters
Note: vCore for AWS
does not use the
following CLI
commands:
restore hostname
restore network
| network]
Whitelist rules rely on normal service shutdown to be backed up.Powering off a VM
directly will lose the whitelist state as rules cannot be saved in that case.
The following example restores the system.
JATP# restore
Example
server
Table 2-16 server
Description
Product(s) CLI All-in-One | Collector | Core/CM | Mac Mini Mac OS X
Mode(s) Basic
Syntax
Sub-Commands
20 Copyright© 2018, Juniper Networks, Inc.
This next example restores the SSH login “support” password to the default.
JATP # restore support password
Restore the default support password? (Yes/No)? yes
support password was restored successfully!
Enters the server configuration mode.
See Also: collector
server
; help; history; ifrestart; ping; reboot; restore; set (server mode);upgrade
exit
Whitelist rules rely on normal service shutdown to be backed up.Powering off a VM
directly will lose the whitelist state as rules cannot be saved in that case.
Page 29
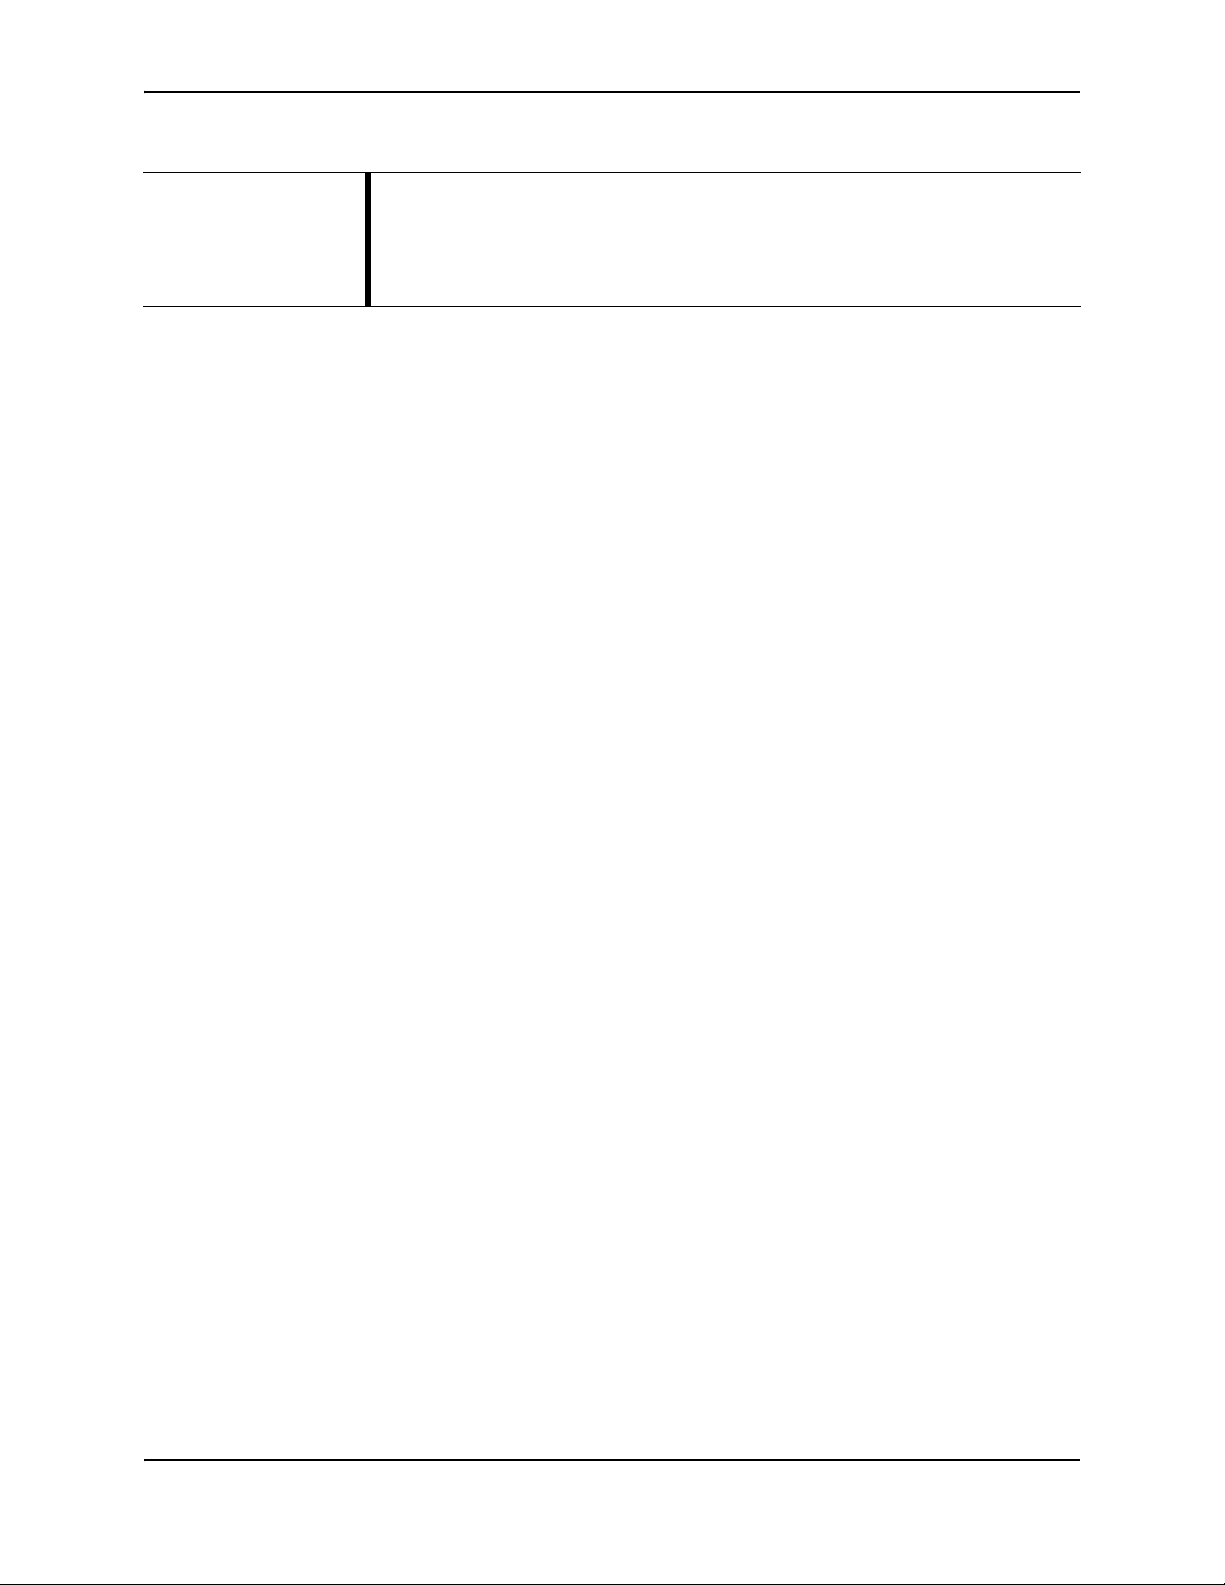
Table 2-16 server
CLI Command Reference Guide
The following example enters server configuration mode:
Example
hostname # server
hostname (server) # ?
Copyright© 2018, Juniper Networks, Inc. 21
Page 30
Juniper Advanced Threat Prevention Appliance
set honeypot (collector mode)
Table 2-17 set honeypot
Enables and disables the SSH-Honeypot feature for a Traffic Collector.
A honeypot can be deployed within a customer network to detect network activity
generated by malware attempting to infect or attack other machines in a local area
network. These attempted SSH logins can be used to supplement detection of
lateral spread.
Description
Product(s) CLI All-in-One | Collector
Mode(s) collector
There are two parameters that can be set for a honeypot:
• Enable/disable a honeypot
• Set a Static IP (IP, mask, and gateway) or DHCP of a publicly addressable interface
See Also:
show honeypot command in show (collector mode)
(collector)# set honeypot ssh-honeypot enable dhcp
Syntax
(collector)# set honeypot ssh-honeypot enable address (IP
address) netmask (subnet IP) gateway (IP address)
(collector):# set honeypot ssh-honeypot disable
The following example enables the SMB parser for lateral detections:
(collector)# set honeypot ssh-honeypot enable
address 1.2.3.4 netmask 255.255.0.0 gateway
Example
1.2.3.1
NOTE The static IP configuration does not require configuring DNS.
Honeypots do not require a DNS server at this time.
set traffic-monitoring (for JATP700 Appliances only) (collector mode)
Table 2-18 set traffic-monitoring
Description Sets the traffic monitoring interface on the JATP700
Product(s) CLI All-in-One | Collector
Mode(s) collector
# set traffic-monitoring-ifc 1gb_ifc
Set the traffic monitoring interface to be the 1G interface.
# set traffic-monitoring-ifc 10gb_ifc
Syntax
22 Copyright© 2018, Juniper Networks, Inc.
Set the traffic monitoring interface to be the 10G interface.
NOTE After making an interface type change, the system must be rebooted
for the change to take effect.
Page 31
set traffic-filter (collector mode)
traffic-filter add
<RuleString><Dom
ainString><sourceaddress>
<destin
ation-address>
<source-port>
<destinationport>
<protocol>
Adds a traffic filter rule where:
“RuleString” is the name of the rule
“DomainString” is the domain to filter out
“source-address” is the source IPv4 address or network
(CIDR)
“destination-address” is the destination IPv4 address or
network (CIDR)
“source-port” is the source port number (0-65535)
“destination-port” is the destination port number (0-65535)
“protocol” is the protocol type: either IP, TCP, UDP or HTTP
Table 2-19 set traffic-filter
Sets traffic filter rules to avoid analysis on a set of configured traffic, which cannot
be made retroactive; for example: any analysis skipped as a result of the filtering
Description
Product(s) CLI All-in-One | Collector
Mode(s) collector
cannot be reversed. This command can be applied to an entire network/subnet/
CIDR range.
See Also: set (server mode)
set traffic-filter {add <rule_name> <domain> <source-
Syntax
address> <destination-address> <source-port>
<destination-port> <protocol> | remove <rule_name>}
Parameters
CLI Command Reference Guide
; show (diagnosis mode) [show traffic-filter]
Example
set protocols (collector mode)
Table 2-20 set protocols
Description
Product(s) CLI All-in-One | Collector
Mode(s) collector
Syntax
Example
The following example add a traffic filter rule to the Traffic Collector.
JATP-collector02(collector)# set traffic-rule add
CustomRule2 headqrts.example.com 10.2.00/16 20.0.0.2
90 120 tcp
where destination-address is 20.0.0.2, destination-port is 120, protocol is tcp,
source-address is 10.2.0.0/16 and source-port is 90 (in our example).
Enables and disables the HTTP or SMB parser for a Traffic Collector.
See Also:
show protocols command in show (collector mode)
(collector)# set protocols {http [on|off] | smb [on|off]}
The following example enables the SMB parser for lateral detections:
hostname (collector) set protocols smb on
Copyright© 2018, Juniper Networks, Inc. 23
Page 32
Juniper Advanced Threat Prevention Appliance
inside Sets the inside proxy IP addresses
outside Sets the outside proxy IP addresses
add Adds a proxy configuration.
remove Removes a proxy configuration.
set proxy (collector mode)
Table 2-21 set proxy
Sets an Inside or Outside data path proxy from collector mode.
Deploy Traffic Collectors in locations where the monitoring interface is (1) placed
“outside” between the proxy and the egress network for customer environments in
which the proxy supports XFF (X-Forwarded-For), or (2) [the more typical
deployment scenario], the Collector is placed between the proxy and the internal
network using FQDN (if available) to identify the threat source for all types of
incidents (“inside” proxy). When configured, the Juniper ATP Appliance Traffic
Collector will monitor all traffic and correctly identify source and destination hosts
for each link in the kill chain wherever the data allows for it.
Note that if the “X-Forwarded-For” header is provided in the HTTP request,
detection will identify threat targets when deployed outside of the proxy
Description
(customers can choose to disable the XFF feature in the proxy setting, if desired).
See Also: set (server mode)
(diagnosis mode);
NOTE The mitigation IP address of a CNC server is not be available for Inside
proxy deployments. When a Juniper ATP Appliance is deployed behind a proxy,
the Mitigation-> Firewall page in the Juniper ATP Appliance Central Manager
Web UI (which typically displays the CNC server IP address to mitigate) will be
empty. The destination IP address of any callback is made to the proxy server
ip address, so it is not relevant to display the proxy server IP address on the
Mitigation->Firewall page.
[“set proxy” command for management network]; set
Product(s) CLI All-in-One | Collector
Mode(s) collector
set proxy inside {add <proxy IP address> <proxy port> |
remove <proxy IP address> <proxy port>
Syntax
set proxy outside {add <proxy IP address> | remove <proxy
IP address>
Parameters
The following example sets an inside data path proxy:
JATP (collector)# set proxy inside add 10.1.1.1 8080
Example
The following example sets an outside data path proxy:
JATP (collector)# set proxy outside add 10.2.1.1
24 Copyright© 2018, Juniper Networks, Inc.
Page 33
set (diagnosis mode)
all Sets logging for all Juniper ATP Appliance components.
default Sets logging to the default parameters
debug Sets logging at the debug level.
info Sets logging at the info level.
warning Sets logging at the warning level.
error Sets logging at the error level.
critical Sets logging at the critical level.
Table 2-22 set
CLI Command Reference Guide
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Example
Sets the logging levels for Juniper ATP Appliance components from diagnosis mode.
See Also: set (server mode)
; set (collector mode)
set logging
The following example sets the default logging level for all Juniper ATP Appliance
components.
JATP# set logging all
Copyright© 2018, Juniper Networks, Inc. 25
Page 34
Juniper Advanced Threat Prevention Appliance
dhcp Enables DHCP for the management or alternate-exhaust
interface.
address Sets the static IP address for the management (eth0) or
alternate-exhaust (eth2) interface,
netmask Sets the netmask for the management network or the
alternate-exhaust network.
gateway Sets the Gateway IP address for the management interfac
or the optional alternate-exhaust network.
set ip interface (server mode)
Table 2-23 set ip interface
Sets the management interface (eth0) and/or the alternate-exhaust interface
(eth2) for the Juniper ATP Appliance.
Description
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) server
Refer to the Operator’s Guide for information about configuring the optional
alternate analysis engine eth2 interface option (it moves CnC traffic during analysis
engine processing off the enterprise’s eth0 management network).
See Also: set (server mode)
shutdown
; set protocols (collector mode); show (core mode);
(server) # set ip interface management <dhcp | address |
netmask | gateway>
Syntax
(server) # set ip interface alternate-exhaust <address |
netmask | gateway>
Parameters
Example
The following example configures the management interface (eth0) for a Juniper
ATP Appliance Core device:
JATP (server)# set ip interface management address
10.2.123.18 netmask 255.255.255.0 gateway 10.2.0.1
The following example configures the management interface (eth0) using DHCP:
JATP (server)# set ip interface management dhcp
This example configures the alternate-exhaust interface (eth2) for a Juniper ATP
Appliance Core device:
JATP (server)# set ip interface alternate-exhaust
address 10.2.123.12 netmask 255.255.255.0 gateway
10.2.0.2
26 Copyright© 2018, Juniper Networks, Inc.
Page 35
CLI Command Reference Guide
set (server mode)
Table 2-24 set
Description Configure the system settings.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server, See Also: set (diagnosis mode)
set [autoupdate {on | off} | cli timeout secs | clock | cm
address | support {enable | disable} localmode {enable |
disable}| passphrase string | dns | firewall {all <backup
Syntax
| flush> | whitelist} | hostname string | ip interface
{management | alternate-exhaust}| ntpserver | password |
proxy {config | enabled | remove} | timezone string |
uipassword]
Note: vCore for AWS does not use the following CLI commands:
set ip
Parameters
(Columns below)
autoupdate
{content |
set hostname
[Users cannot set static IP address or change the hostname directly on an EC2 AWS
instance]
server mode “set proxy” command is a management network proxy tool; for data
path Collector proxy configurations, refer to
set proxy (collector mode)
Turn on or off automatic product updates.
set autoupdate content on
software} {on |
off}
; set traffic-filter (collector mode)
cli timeout secs
clock
cm address
set support
{enable
| disable} |
{localmode}
dns
firewall {all
<backup | flush>
| whitelist <add
| delete |
flush>}
Sets CLI timeout period in seconds (0 indicates
no timeout).
Sets the current date and time.
Sets the IP address of the Central Manager and
netmask using the slash notation; example:
AAA.BBB.CCC.DD/X
Enables remote SSH login “support” account or
localmode enable|/disable.
Sets DNS (or enables DHCP for DNS) for the management interface by default if interface is unspecified.
Backs up or flushes (clears) all current iptables
for a firewall, or adds, deletes or flushes the
current iptables whitelist-specific settings for the
firewall.
The “add” option adds an IP address to the
iptables outbound whitelist.
# set firewall whitelist add
10.1.1.1
Copyright© 2018, Juniper Networks, Inc. 27
Page 36
Juniper Advanced Threat Prevention Appliance
Table 2-24 set
hostname string Sets the system’s host name.
ip interface
{management |
alternate-
Sets the IP address, netmask, or default gateway,
or enables DHCP for the management or
alternate-exhaust interface.
exhaust} <dhcp |
address |
netmask |
gateway}
ntpserver
Sets the Network Time Protocol (NTP) server.
passphrase string Sets the device key password; enter a string.
password
proxy {config
Sets a new password for the CLI administrator.
Config, enable/disable, or remove “all” proxy configs,
or remove an HTTP-specific proxy server.
<all|http> |
enabled <on|off>
| remove
<all|http>}
timezone string
uipassword
Sets the timezone for the device.
Sets a new admin password for CM Web UI access.
TIP Tip: Config the proxy for “all” protocols first, and
then change HTTP proxy as needed.
Example
The following example disables the CLI timeout counter.
JATP (server)# set cli timeout 0
The following example enables support:
JATP (server)# set support enable
28 Copyright© 2018, Juniper Networks, Inc.
Page 37
set system-alert (server mode)
Table 2-25 set system-alert
Configure the traffic threshold and checking interval for the Collector “monitored
traffic” health status.
Description
Product(s) CLI All-in-One | Core CM
When the monitored traffic of a collector within the checking interval time is lower
than the threshold, a system health alert is generated. You can send an email
notification of the alert if email notifications of system health events are
configured.
CLI Command Reference Guide
Mode(s) Server, See Also: set (diagnosis mode)
set system-alert traffic <integer> time <interval>
Syntax
Parameters
NOTE Note that both "traffic" and "time" parameters are required in order to
set the threshold for both the minimum traffic and time.
traffic - the minimum traffic (in KB)
interval - the checking interval (in minutes)
JATP (server) # set system-alert traffic 100 time 30
This example sets the system alert such that, if the total monitored traffic of a
collector within the last 30 minutes dips lower than 100KB, then a system health
alert will be generated (and users will receive an email notification of the alert if
email notifications are configured for system health events).
Example
By default this alert is disabled, and users must set the minimum traffic and interval
in order to enable it. Also note that all bytes seen on Ethernet frames are counted in
the traffic.
The minimum interval for the "set system-alert traffic" time interval command is 10
minutes. If the minimum interval is set to less than 10 minutes, no alerts will be
triggered.
; set traffic-filter (collector mode); show
Copyright© 2018, Juniper Networks, Inc. 29
Page 38
Juniper Advanced Threat Prevention Appliance
all Checks both basic settings and analysis pipelin
report Shows report of last setupcheck.
basic Checks basic configuration settings.
analysis Checks the analysis pipeline.
setupcheck
Table 2-26 setupcheck
Description Checks and reports on basic configuration settings and analysis pipeline setup.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Example
setupcheck {all | report | basic | analysis}
The following example checks all basic configuration settings as well as the
analysis pipeline:
JATP (diagnosis) # setupcheck all
30 Copyright© 2018, Juniper Networks, Inc.
Page 39
show (collector mode)
traffic-filter
Shows all traffic filter rules.
protocols
Shows current HTTP or SMB protocol parser settings
proxy {inside
|outside}
Shows Traffic Collector proxy for inside or outside
configurations.
honeypot Shows the current honeypot configuration.
Table 2-27 show (collector mode)
CLI Command Reference Guide
Description
Product(s) CLI All-in-One | Collector
Mode(s) Collector
Subcommands
Syntax
Parameters
Displays the Traffic Collector HOMENET settings and all configured subnets, as well
as current traffic filters and the current XFF status (enabled or disabled)
homenet | traffic-filter | proxy | honeypot
show
The following example displays the current Collector proxy inside settings:
collector02(collector)# show proxy inside
Proxy IPs: 10.1.1.1
The following example displays the current traffic filter:
collector02 (collector)# show traffic-filter
Example
Name: CustomRule2, Domain: headqtrs.example.com
The following example displays the current SMB protocol parser setting:
collector02 (collector)# show protocols
The following example displays the current honeypot configuration:
collector02 (collector)# show honeypot ssh-honeypot
show (collector mode)
Table 2-28 show (collector mode)
Description
Product(s) CLI All-in-One | Collector
Mode(s) Collector
Display the currently selected traffic monitoring interface.
collector02 (collector)#ow traffic-monitoring-ifc-type
Syntax
Display the currently selected traffic monitoring interface
Copyright© 2018, Juniper Networks, Inc. 31
Page 40
Juniper Advanced Threat Prevention Appliance
images Displays guest image update and status
information.
whitelist Displays the name, hit count and the time of last
hit of a user configured whitelist.
Note that when a whitelist rule is deleted, it will be
removed from the list. Updates to existing rule are
not affected by the presence of the rule in the
output, but hit count could increment. Further,
more than one rule can be hit by a single incident.
alternate-exhaustinterface
Displays the status of the alternate exhaust
interface eth2.
show (core mode)
Table 2-1
Description
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) Core
Syntax
Parameters
Displays the guest image(s) status or whitelist statistics.
See Also: shutdown
; show (diagnostic mode)
show
The following example demonstrates the show images command usage:
JATP(core)# show images
The following example demonstrates the show whitelist command usage:
JATP(core)# show whitelist
JATP(core)# show whitelist
Example
Rule Name Hit Count Local Time of Last Hit
URI1 10 Wed Sep 2 18:16:55 2015
URI2 10 Wed Sep 2 18:16:55 2015
URI3 10 Wed Sep 2 18:16:55 2015
greatfilesarey 49 Wed Sep 2 18:20:00 2015
The following example shows how to get the alternate-exhaust interface (eth2)
status:
JATP(core)# show alternate-exhaust interface
32 Copyright© 2018, Juniper Networks, Inc.
Page 41
show (diagnosis mode)
device
{collectorstatus | |
corestatus |
slavecorestatus}
Display connected device statistics for Traffic
Collector, CoreCM, or Mac Mini Detection Engine
Secondary “slave core.”
protocol {web |
email}
Displays the session counts for network web or
email protocols.
objects Displays the current number of file objects.
logging Displays the currently-configured logging level.
See Also: set traffic-filter (collector mode) logging
log error traceback Displays only the tracebacks (if any) generated by
Juniper ATP Appliance OS process error logs. A
traceback is a stack of functions that were
executing when an error condition was
encountered.
log error last
<integer: number of
lines to display>
Displays n [1-1000] lines of the contents of the
common log file.
Example: show log error last 12
Table 2-29 show
CLI Command Reference Guide
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Sets the logging levels for Juniper ATP Appliance components from diagnosis mode.
See Also: shutdown
; show (core mode)
show
The following example displays the connected Traffic Collector status.
JATP(diagnosis)# show device collectorstatus
<cr>
JATP (diagnosis)# show device collectorstatus
WEB_COLLECTOR
=====================================================
====
IP : 10.2.9.68
Enabled : True
Last Seen : 2015-07-25 15:13:17.967000-07:00
Example
Install Date : 2015-06-25 19:03:38-07:00
=====================================================
====
IP : 10.2.20.3
Enabled : True
Last Seen : 2015-07-28 11:07:42.046000-07:00
Install Date : 2013-11-14 09:25:39-08:00
This example displays the log error traceback
JATP(diagnosis)# show log error traceback
<cr>
Copyright© 2018, Juniper Networks, Inc. 33
Page 42
Juniper Advanced Threat Prevention Appliance
-h unsigned integer Specifies the number of hops
string Names the remote system to be traced.
<String_URI> Specifies the software packages to copy .from a remo
location for upgrading via the Core.
shutdown
Table 2-30 shutdown
Description Shuts down the Juniper ATP Appliance server.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
shutdown
None
The following example performs a shutdown of the current device.
JATP# shutdown
traceroute
Table 2-31 traceroute
Description Displays the route packets trace to a host name or an IP address.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server | Collector
Syntax
Parameters
Example
traceroute
The following example performs a traceroute of the named device.
JATP# traceroute -h 2 MacMininOSX-Engine
upgrade
Table 2-32 upgrade
Description
Product(s) CLI All-in-One | Core CM
Mode(s)
Syntax
Parameters
Example
34 Copyright© 2018, Juniper Networks, Inc.
Upgrade Juniper ATP Appliance software for the Core/CM device or vCore, and all
connected physical or virtual devices.
cm
upgrade <URI as user@hostname:path>
The following example copies Juniper ATP Appliance software to the Core from a
remote location defined by the path provided.
CoreCM(cm)# upgrade [email protected]:some/remote/
directory
Page 43
updateimage
built-in Updates the guest-image on the detection Engine.
Table 2-33 updateimage
Update or correct the guest-image OS profile used by the detection and analysis
Description
Product(s) CLI All-in-One | Core-CM | Mac Mini OS X Detection Engine
Mode(s) Core
behavioral engine.
The updateimage command will update the guest images from the Juniper ATP
Appliance update servers or a USB drive attached to the Juniper ATP Appliance.
CLI Command Reference Guide
Syntax
Parameters
Example
wizard
Table 2-34 wizard
Description
updateimage
The following example performs a built-in profile update for the Core detection
engine.
JATP (core)# updateimage built-in
Installing image SC-XP-20150617.img...
Previous version of SC-XP-20150617.img exists.
Checking integrity...
Image SC-XP-20150617.img is already installed
Installing image SC-W7-20150521.img...
Previous version of SC-W7-20150521.img exists.
Checking integrity...
Image SC-W7-20150521.img is already installed
Enters the Configuration Wizard. For Configuration Wizard commands and
response, see “Configuration Wizard for the All-in-One Server” in the next section to
follow command prompts and recommended responses.
Product(s) CLI All-in-One | Core/CM | Collector | Mac Mini Mac OS X
Mode(s) Basic
Syntax
Parameters None
Example
wizard
The following command starts the configuration wizard.
hostname # wizard
Copyright© 2018, Juniper Networks, Inc. 35
Page 44
Juniper Advanced Threat Prevention Appliance
Configuration Wizard for the All-in-One Server
Table 2-35 Configuration Wizard for All-in-One Server
Configuration Wizard Prompts Customer Response Actions
Use DHCP to obtain the IP address and DNS
server address for the administrative interface
(Yes/No)?
Note: Only if your DHCP response is no,enter
the following information when prompted:
a. IP address (no CIDR format)
b. Netmask
c. Enter a gateway IP address for this
management (administrative) interface:
d. Enter primary DNS server IP address.
e. Do you have a secondary DNS Server
(Yes/No).
f. Do you want to enter the search
domains?
g. Enter the search domain (separate
multiple search domains by space):
Restart the administrative interface (Yes/No)?
Enter a valid hostname. Type a hostname when prompted; do not
[OPTIONAL]
If the system detects a Secondary Core with an
eth2 port, then the alternate CnC exhaust
option is displayed:
Use alternate-exhaust for the analysis engine
exhaust traffic (Yes/No)?
Enter IP address for the alternate-exhaust
(eth2) interface:
Enter netmask for the alternate-exhaust (eth2)
interface: (example: 255.255.0.0)
Enter gateway IP Address for the alternateexhaust (eth2) interface: (example:10.6.0.1)
Enter primary DNS server IP Address for the
alternate-exhaust (eth2) interface: (example:
8.8.8.8)
Do you have a secondary DNS server for the
alternate-exhaust (eth2) interface?
Do you want to enter the search domains for
the alternate-exhaust (eth2) interface?
Note: A complete network interface restart can
take more than 60 seconds
We strongly discourage the use of DHCP
addressing because it changes dynamically. A
static IP address is preferred.
Recommended: Respond with no:
a. Enter an IP address
b. Enter a netmask using the form
255.255.255.0.
c. Enter a gateway IP address.
d. Enter the DNS server IP address
e. If
yes enter the IP address of the secondary
DNS server.
f. Enter
specific domain.
g. Enter search domain(s) separated by spaces;
for example: example.com lan.com dom2.com
Enter
settings applied.
include the domain; for example: JuniperATP1
Refer to “Configuring an Alternate Analysis
Engine Interface” in the Juniper ATP Appliance
Operator’s Guide for more information.
Enter yes to configure an alternate eth2
interface.
Enter the IP address for the eth2 interface.
Enter the eth2 netmask.
Enter the gateway IP address.
Enter the primary DNS server IP Address for the
alternate-exhaust (eth2) interface.
Enter yes or no to confirm or deny an eth2
secondary DNS server.
Enter yes or no to indicate whether you want to
enter search domain.
yes if you want DNS lookups to use a
yes to restart with the new configuration
Regenerate the SSL self-signed certificate
(Yes/No)?
36 Copyright© 2018, Juniper Networks, Inc.
Enter yes to create a new SSL certificate for
the Juniper ATP Appliance Server Web UI.
Page 45
This chapter describes the commands for available for Juniper ATP Appliance Core/CM or vCore servers. These
CHAPTER 3
Core/CM Server CLI Commands
commands are used to configure devices and software, manage security events, and show system information
and status.
You must enclose non-alphabet characters in double quotes in CLI commands.
Basic Mode Commands
Use general system commands to configure the appliance, view appliance history, enter other CLI modes, obtain
help with CLI syntax, and to exit the CLI session.
The general commands are:
• cm on page 39
• core on page 40
• diagnosis on page 41
• exit on page 42
• help on page 43
• history on page 44
• server on page 48
• wizard on page 59
Refer to the respective sections in this guide to review Diagnosis Mode, CM Mode, Collector Mode and Server
Mode commands per product device.
CM Commands
• exit on page 42
• help on page 43
• history on page 44
• upgrade on page 58
Copyright© 2018, Juniper Networks, Inc. 37
Page 46
Juniper Advanced Threat Prevention Appliance
Core Mode Commands
• exit on page 42
• help on page 43
• history on page 44
• set (core mode) on page 48
• show (core mode) on page 53
• updateimage on page 59
Server Mode Commands
• exit on page 42
• help on page 43
• history on page 44
• ifrestart on page 44
• ping on page 45
• reboot on page 45
• restart on page 45
• restore on page 47
• set (server mode) on page 50
• server on page 48
• show (server mode) on page 55
• shutdown on page 58
• traceroute on page 58
• upgrade on page 58
Diagnosis Mode Commands
• capture-start on page 39
• copy on page 41
• exit on page 42
• gssreport on page 42
• help on page 43
• history on page 44
• set (diagnosis mode) on page 52
• setupcheck on page 52
• show (diagnosis mode) on page 54
38 Copyright© 2018, Juniper Networks, Inc.
Page 47
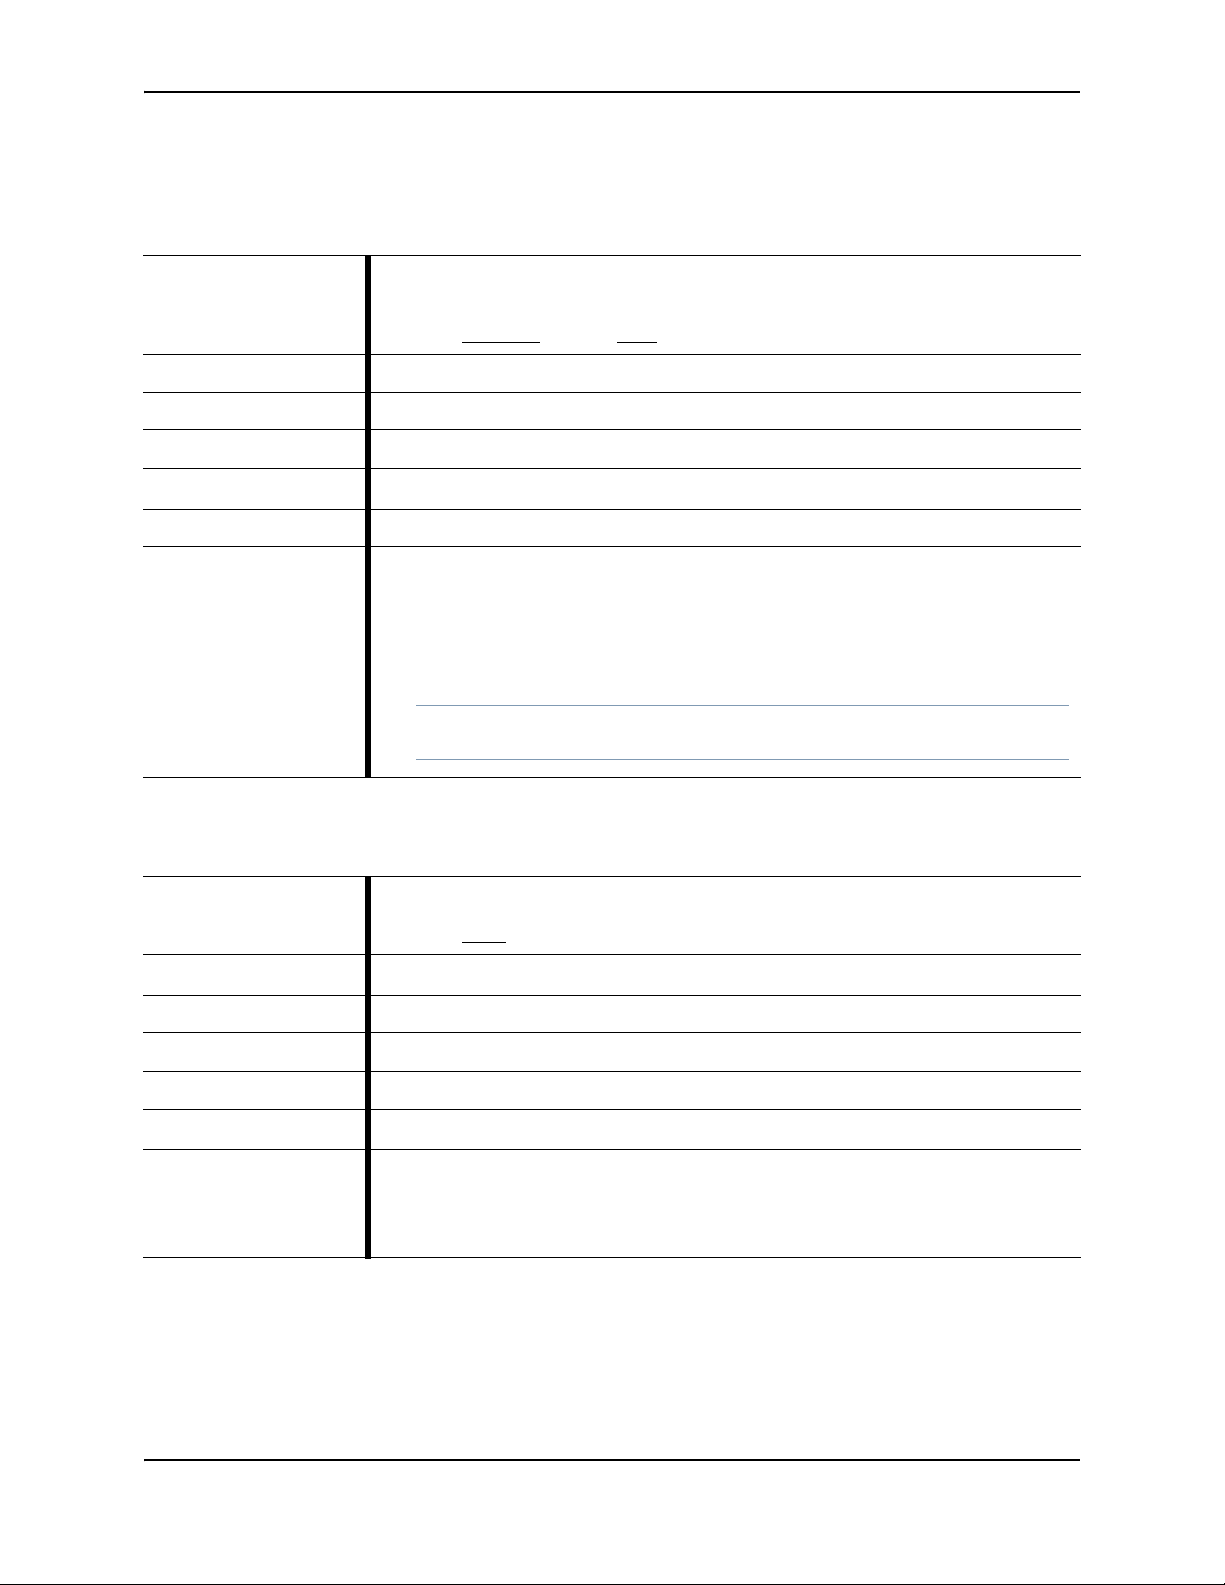
CLI Command Reference Guide
CoreCM CLI Commands
capture-start
Table 3-1 capture-start
Starts packet capture as a means for diagnosing and debugging network traffic and
Description
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Diagnosis
obtaining stats (not part of the Collector traffic capture engine).
See Also: diagnosis
[mode]; copy
Syntax
Parameters
Sub-Commands None
capture-start
<IP address> <interface_name>
The following example starts a packet capture process on interface eth1 for a
Juniper ATP Appliance with IP address 8.8.8.8:
hostname # diagnosis
Example
cm
Table 3-2 cm
Description
Product(s) CLI
Mode(s) Basic
hostname (diagnosis)# capture-start 8.8.8.8 eth1
Enters cm (Central Manager) mode.
See Also: basic
All-in-One | Core
NOTE Address 8.8.8.8 need not be a Juniper ATP Appliance. It is just a host
that the capture filters on.
[mode];
Syntax
Parameters None
Sub-Commands
Example
cm
exit | help | history | upgrade
The following command example enters cm configuration mode:
hostname # cm
hostname (cm)#
Copyright© 2018, Juniper Networks, Inc. 39
Page 48
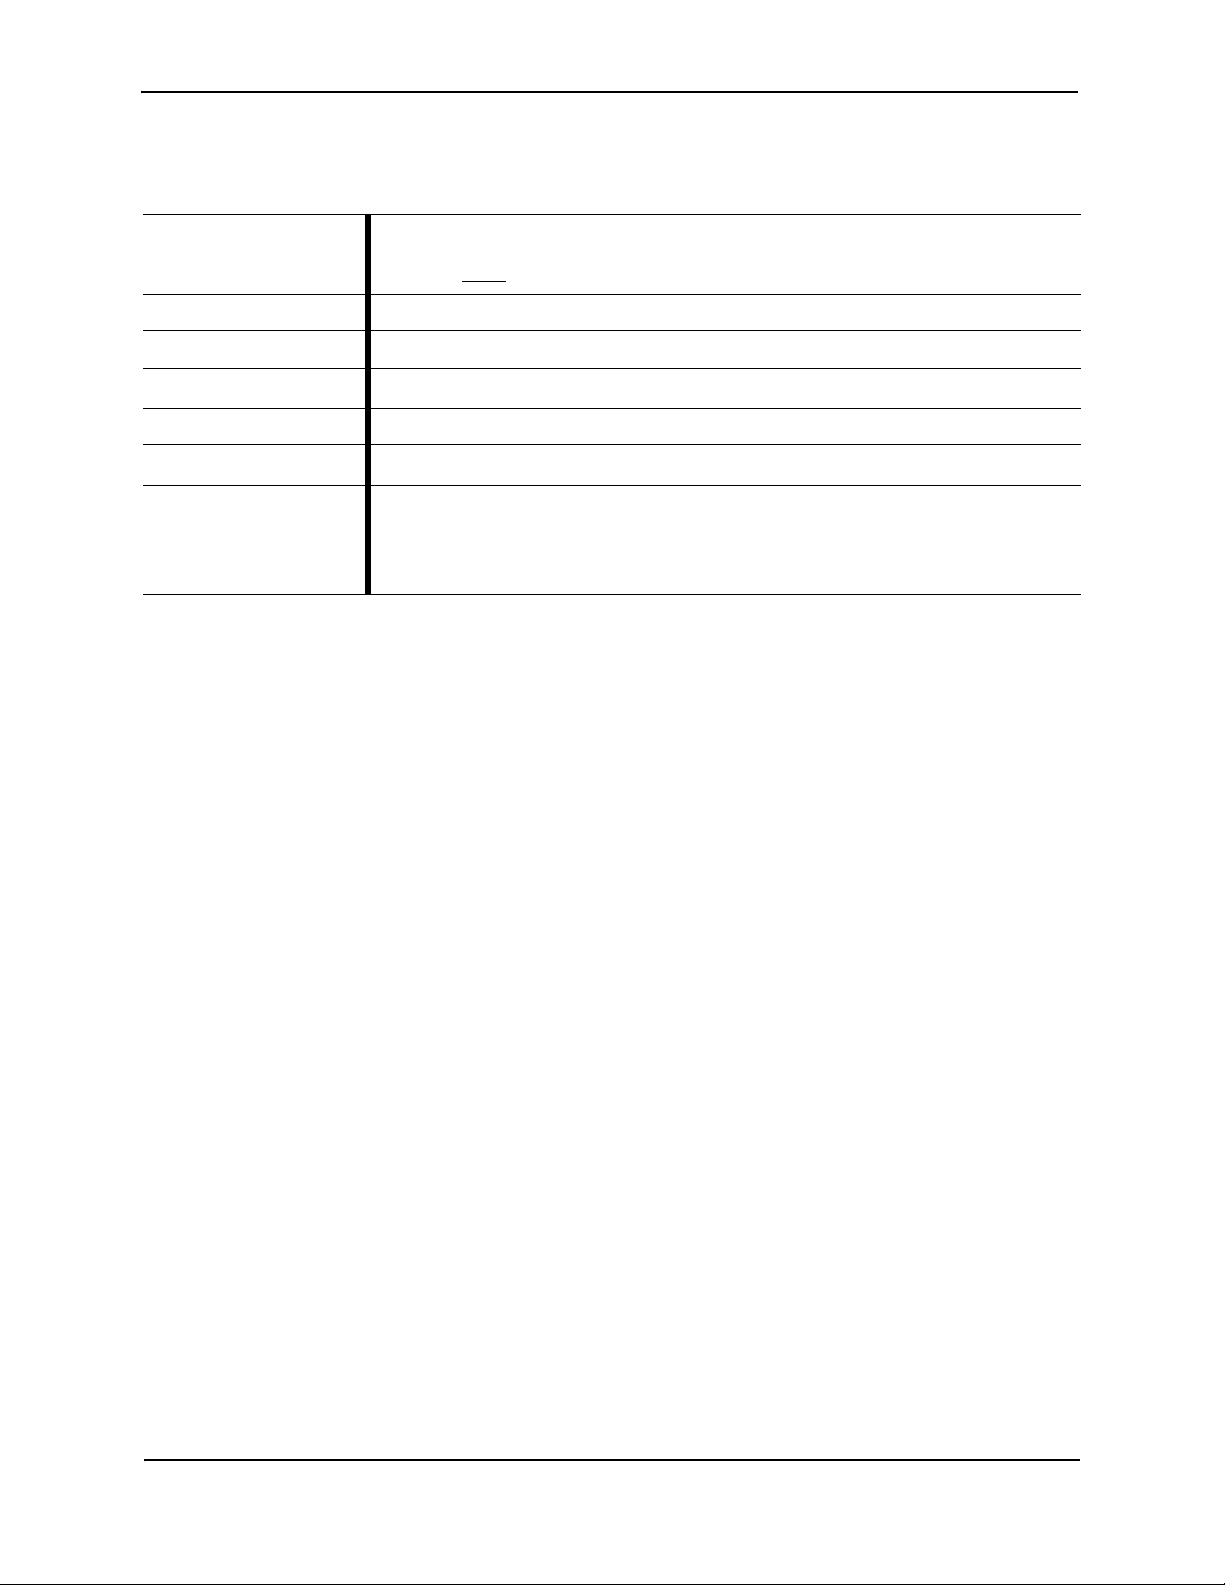
Juniper Advanced Threat Prevention Appliance
core
Table 3-3 core
Enters core mode.
Description
See Also: basic
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Basic
[mode];
Syntax
Parameters None
Sub-Commands
Example
core
exit | help | history | set | show | updateimage
The following command example enters core configuration mode:
hostname # core
hostname (core)#
40 Copyright© 2018, Juniper Networks, Inc.
Page 49
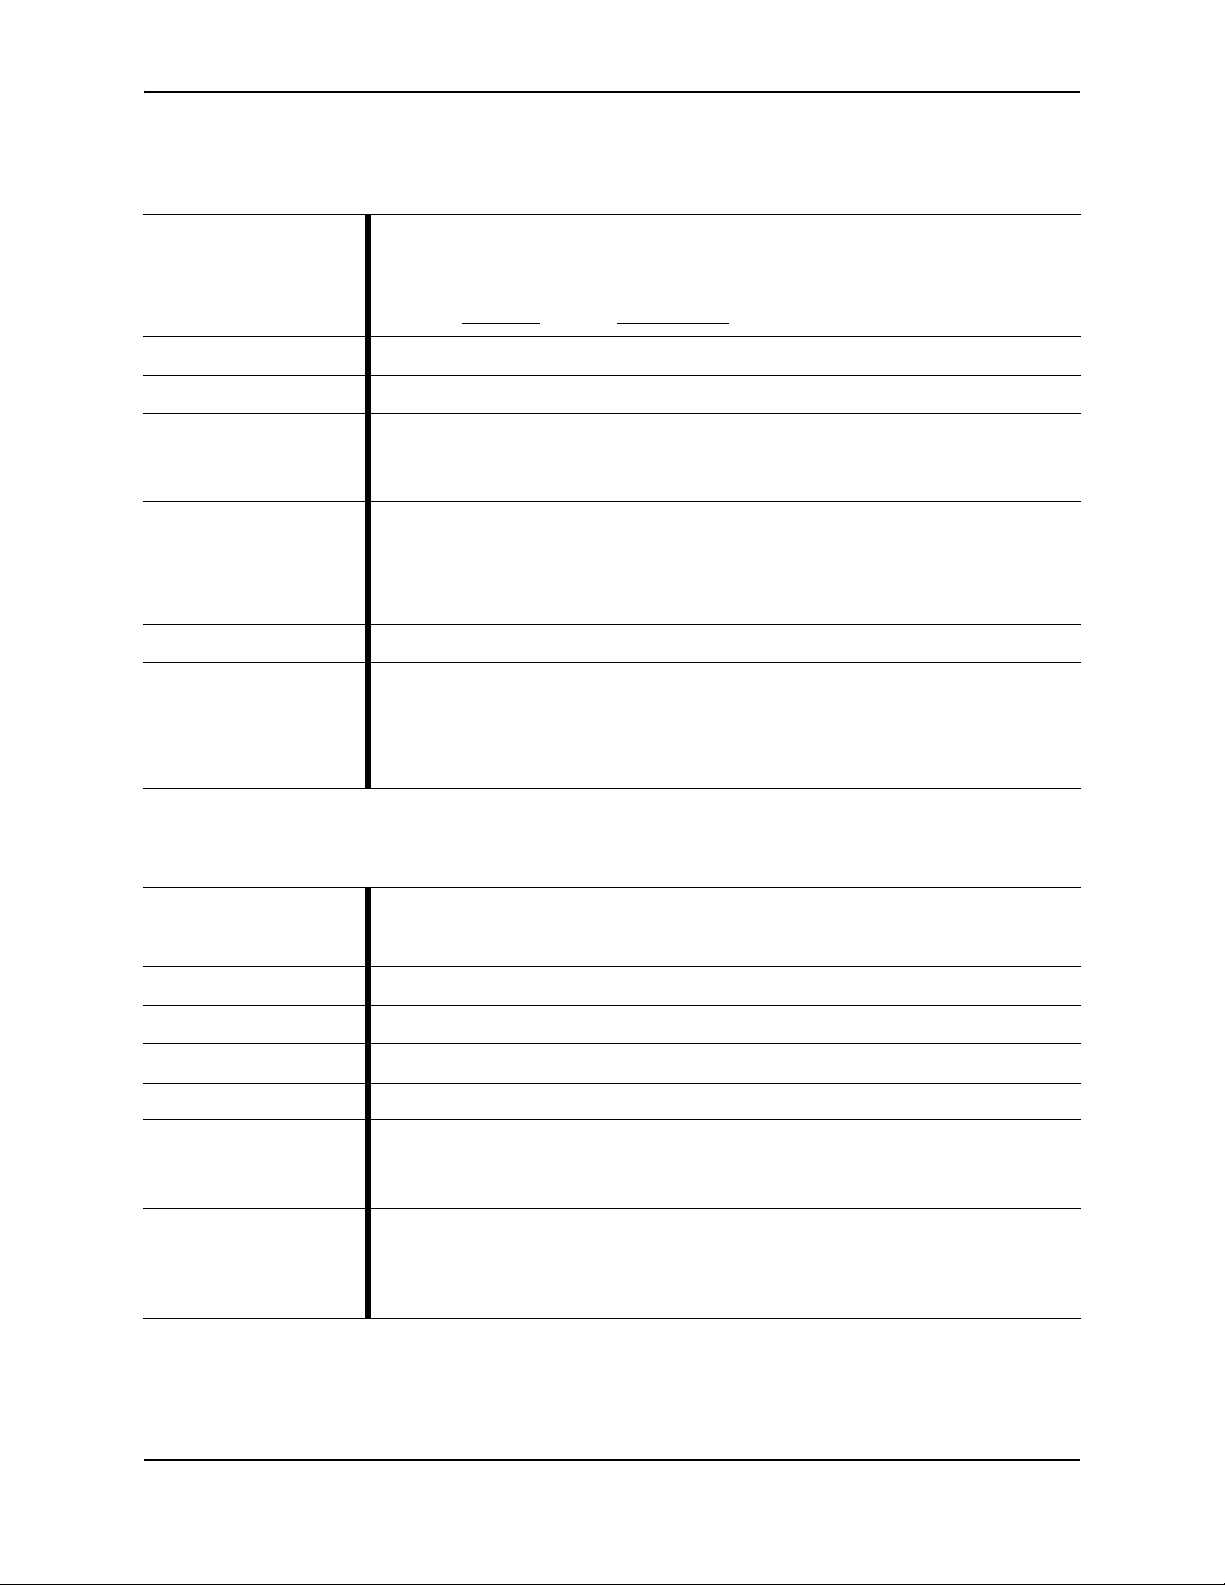
copy
Table 3-4 copy
Description
CLI Command Reference Guide
Uses Secure Copy (SCP) to scp to copy and transfer packet capture or traceback
(crash) data to a remote location, providing the same authentication and level of
security as an SSH transfer.
See Also: diagnosis
Product(s) CLI
Mode(s) Diagnosis
All-in-One | Collector | Core | Mac OS X Detection Engine
copy capture <scp source_file_name
Syntax
username@destination_host:destination_folder> | traceback
all <string URI as user@hostname:path>
copy capture <scp remote filename_location>
Parameters
copy traceback all <path string>
copy traceback <tab> [tab displays all available crash
filenames]
Sub-Commands None
The following example copies the file "captureEth1.txt" from the local host to a
remote host:
Example
hostname (diagnosis)# copy capture scp captureEth1.txt
[email protected]:/some/remote/directory
diagnosis
Table 3-5 diagnosis
[mode]; capture-start
Enters the Diagnosis configuration and status check mode.
Description
See Also: collector [mode], server [mode]
Product(s) CLI
Mode(s) Basic
Syntax
Parameters None
All-in-One | Collector | Core | Mac OS X Detection Engine
diagnosis
capture-start; copy; exit; gssreport; help; history; set
Sub-Commands
(server mode); setupcheck; show (diagnosis mode); show
(server mode)
The following example enters diagnosis configuration and status check mode:
Example
hostname # diagnosis
hostname (diagnosis)# ?
Copyright© 2018, Juniper Networks, Inc. 41
Page 50
Juniper Advanced Threat Prevention Appliance
exit
Table 3-6 exit
Description Ends the CLI session.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Core | CM | Collector | Diagnosis | Server
Syntax
Parameters None
Example
gssreport
Table 3-7 gssreport
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Sub-Commands None
exit
The following example ends the CLI session.
JATP# (diagosis) exit
JATP#
Use the gssreport command to submit reports to Juniper Global Security Services
(GSS), and to display the status of the current GSS report.
See Also: gssreport
; diagnosis [mode]
gssreport status | submit
status - displays the status of the current GSS report.
submit - submits a report to Juniper ATP Appliance GSS.
The following examples display the status of a GSS report submission:
hostname # diagnosis
hostname (diagnosis)# gssreport submit
Successfully started GSS report
Example
hostname (diagnosis)# gssreport status
GSS is currently enabled
Last 5-minute GSS report at 2014-07-28 10:34:24.414322:
successfully submitted
Last hourly GSS report at 2014-07-28 10:34:24.468259:
successfully submitted
Last daily GSS report at 2014-07-28 10:34:28.225512:
successfully submitted
42 Copyright© 2018, Juniper Networks, Inc.
Page 51
CLI Command Reference Guide
help
Table 3-8 help
Description Displays information about the CLI help system.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Core | CM | Collector | Diagnosis | Server
Syntax
Parameters
Example
help
None
The following example shows some of the output of the help command.
CONTEXT SENSITIVE HELP
[?] - Display context sensitive help. This is either a list of
possible command completions with summaries, or the full syntax
of the current command. A subsequent repeat of this key, when a
command has been resolved, will display a detailed reference.
AUTO-COMPLETION
The following keys both perform auto-completion for the current
command line. If the command prefix is not unique then the bell
will ring and a subsequent repeat of the key will display
possible completions.
[enter] - Auto-completes, syntax-checks then executes a command.
If there is a syntax error then offending part of the command
line will be highlighted and explained.
[tab] - Auto-completes
[space] - Auto-completes, or if the command is already resolved
inserts a space.
If “<cr>” is shown, that means that what you have entered so
far is a complete command, and you may press Enter (carriage
return) to execute it.
Use ? to learn command parameters and option:
JATP (server)# show f?
firewall Show the firewall configuration settings
interface
JATP (server)# show firewall?
all Show the current iptables settings
whitelist Show the iptables whitelist settings
show firewall whitelist?
<cr>
show firewall whitelist
Copyright© 2018, Juniper Networks, Inc. 43
Page 52
Juniper Advanced Threat Prevention Appliance
eth0 Restarts the management network administra
interface.
eth1 Restarts the monitoring network interface.
history
Table 3-9 history
Description Displays the current CLI session command line history.
Product(s) CLI
Mode(s) Basic | Core | CM | Collector | Diagnosis | Server
Syntax
Parameters None
Example
All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
history
The following examples returns command line history for the current CLI session.
JATP# history
ifrestart
Table 3-10 ifrestart
Description Restarts the interface driver and services using the interface.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
ifrestart eth0 | eth1
Example
44 Copyright© 2018, Juniper Networks, Inc.
The following example restarts the
<FireEye_name># ifrestart eth0
eth0 interface for the management network.
Page 53
CLI Command Reference Guide
-c count Number of echo requests to send. By default, pings ar
continuously until you press Ctrl+C.
-h hops Number of next hops between pings (default is 1).
string IP address, hostname or interface name used to ping
device address.
ping
Table 3-11 ping
Sends ICMP (Internet Control Message Protocol) echo request packets to a
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
specified host name or IP address to verify that the destination is reachable over
the network.
Syntax
Parameters
Example
reboot
ping [-c count] [-h hops] [string]
The following example sends three echo requests to the device with the IP Address
10.10.10.1
<FireEye_name>#
PING 10.10.10.1 (10.10.10.1) 56(84) bytes of data.
64 bytes from 10.10.10.1: icmp_req=1 ttl=64 time=0.314 ms
64 bytes from 10.10.10.1: icmp_req=2 ttl=64 time=0.277 ms
64 bytes from v: icmp_req=3 ttl=64 time=0.274 ms
--- 10.10.10.1 ping statistics --3 packets transmitted, 3 received, 0% packet loss, time
bbbb1999ms
rtt min/avg/max/mdev = 0.274/0.288/0.314/0.022 ms
ping -c 3 10.10.10.1
Table 3-12 reboot
Description Reboots the Juniper ATP Appliance.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters None
Example
reboot
The following example reboots the system.
hostname# reboot
restart
Table 3-13 restart
Description Restarts Juniper ATP Appliance services.
Copyright© 2018, Juniper Networks, Inc. 45
Page 54
Juniper Advanced Threat Prevention Appliance
all Restarts all Juniper ATP Appliance services.
behaviorengine Restarts the Behavioral Analysis Engine.
cm Restarts the Central Manager Web UI service.
collector Restarts the Collector service.
core Restarts the Core Detection Engine.
correlationengine Restarts the Correlation Engine.
database Restarts the Database.
ntpserver Restarts the NTP server.
sshserver Restarts the SSH server.
staticengine Restarts the Static Analysis Engine.
webserver Restarts the web server.
Table 3-13 restart
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
restart [all | behaviorengine | cm | collector | core |
Syntax
Parameters
correlationengine | database | ntpserver | sshserver |
staticengine | webserver]
The following example restarts the Central manager service.
Example
JATP# restart cm
46 Copyright© 2018, Juniper Networks, Inc.
Page 55
CLI Command Reference Guide
support
Restores the default support password setting for SSH
remote login (set during initial installation per license).
See also (server)# set (server mode) support
firewall
{backup |
default}
Restores the firewall settings from either the previous
backup, or from the default factory settings.
Whitelist rules rely on normal service shutdown to be
backed up.Powering off a VM directly will lose the whitelist
state as rules cannot be saved in that case
hostname
Restores the system’s hostname to the factory default
hostname.
network
Restores the IP address and DNS settings to the
factory default settings.
WARNING: This command option removes the current
IP address and DNS settings, and reloads the default
values for these settings.
restore
Table 3-14 restore
Description Restores the system configuration to the factory default settings.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Note: vCore for AWS
does not use the
following CLI
commands:
restore hostname
restore network
restore [support | firewall {backup | default} | hostname
| network]
The following example restores the system.
JATP # restore
Example
This next example restores the SSH login “support” password to the default.
JATP # restore support password
Restore the default suppport password? (Yes/No)? yes
support password was restored successfully!
Copyright© 2018, Juniper Networks, Inc. 47
Page 56
Juniper Advanced Threat Prevention Appliance
set (core mode)
Table 3-15 set
Description Resets the Secondary Core UUID, if the virtual core is cloned.
Product(s) CLI Core/CM (Virtual Core)
Mode(s) Core (for Virtual Core configurations)
Syntax
Sub-Commands None
Example
set id
The following example sets the Virtual Core appliance id:
hostname # core
hostname (core) # set id
<cr>
server
Table 3-16 server
Description Enters the server configuration mode.
Product(s) CLI All-in-One | Collector | Core/CM | Mac Mini Mac OS X
Mode(s) Basic
Syntax
server
exit; help; history; ifrestart; ping; reboot; restore; set
Sub-Commands
(server mode); show (server mode); traceroute; upgrade
Whitelist rules rely on normal service shutdown to be backed up. Powering off a VM
directly will lose the whitelist state as rules cannot be saved in that case.
The following example enters server configuration mode:
Example
hostname # server
hostname (server) # ?
set system-alert (server mode)
Table 3-17 set system-alert
Configure the traffic threshold and checking interval for the Collector “monitored
traffic” health status.
Description
Product(s) CLI All-in-One | Core CM
Mode(s) Server, See Also: set (diagnosis mode)
48 Copyright© 2018, Juniper Networks, Inc.
When the monitored traffic of a collector within the checking interval time is lower
than the threshold, a system health alert is generated. You can send an email
notification of the alert if email notifications of system health events are
configured.
; set (collector mode); show
Page 57
Table 3-17 set system-alert
CLI Command Reference Guide
set system-alert traffic <integer> time <interval>
Syntax
Parameters
Example
NOTE Note that both "traffic" and "time" parameters are required in order
to set the threshold for both the minimum traffic and time.
traffic - the minimum traffic (in KB)
interval - the checking interval (in minutes)
JATP (server) # set system-alert traffic 100 time 30
This example sets the system alert such that, if the total monitored traffic of a
collector within the last 30 minutes dips lower than 100KB, then a system health
alert will be generated (and users will receive an email notification of the alert if
email notifications are configured for system health events).
By default this alert is disabled, and users must set the minimum traffic and interval
in order to enable it. Also note that all bytes seen on Ethernet frames are counted in
the traffic.
The minimum interval for the "set system-alert traffic" time interval command is 10
minutes. If the minimum interval is set to less than 10 minutes, no alerts will be
triggered.
Copyright© 2018, Juniper Networks, Inc. 49
Page 58
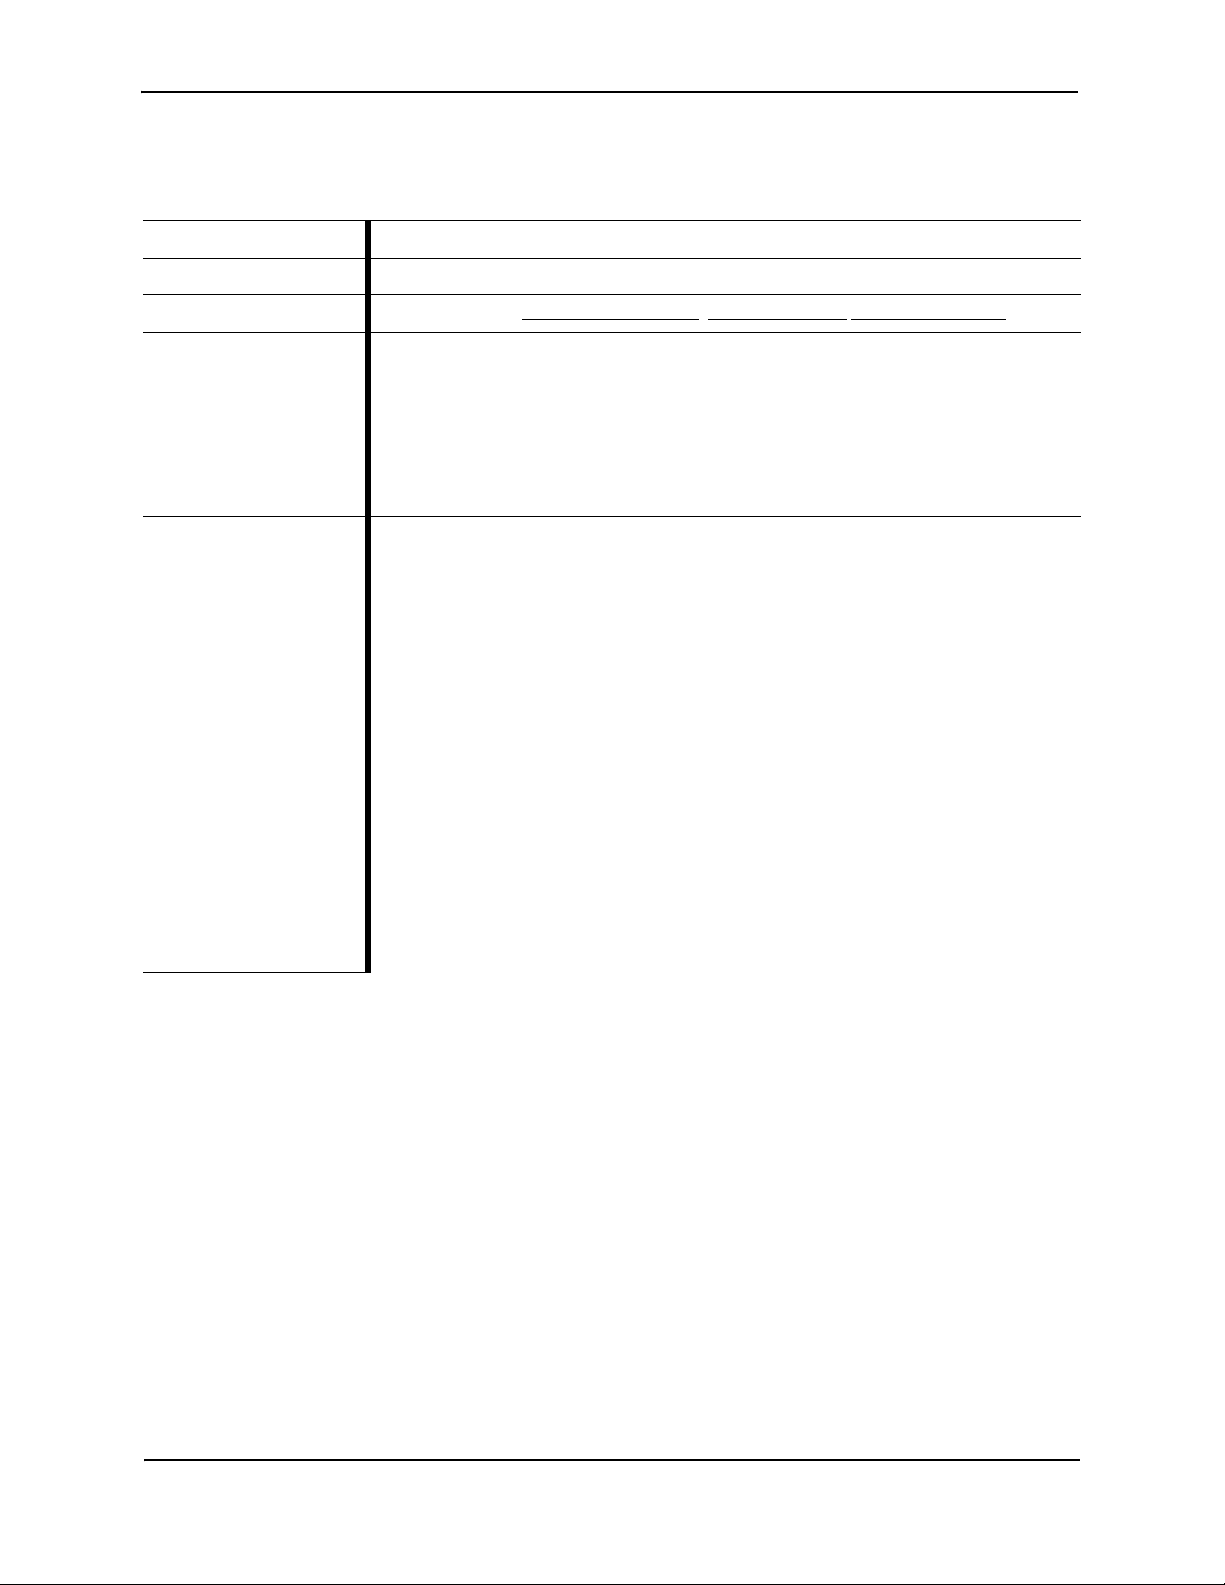
Juniper Advanced Threat Prevention Appliance
set (server mode)
Table 3-18 set
Description Configure the system settings.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server, See Also: set (diagnosis mode)
set [autoupdate {on | off} | cli timeout secs | clock | cm
address | support {enable | disable} localmode {enable |
disable}| passphrase string | dns | firewall {all <backup
Syntax
| flush> | whitelist} | hostname string | ip interface
{management | alternate-exhaust}| ntpserver | password |
proxy {config | enabled | remove} | timezone string |
uipassword]
Parameters
Note: vCore for AWS
does not use the
following CLI
commands:
set ip
set hostname
[Users cannot set static
IP address or change
the hostname directly
on an EC2 AWS
instance]
; set (core mode); show (core mode)
(See columns below)
autoupdate
{content |
Turn on or off automatic product updates.
set autoupdate content on
software} {on |
off}
cli secs
clock Sets the current date and time.
cm address
set support
{enable |
Sets CLI period in seconds (0 indicates
no timeout).
Sets the IP address of the Central Manager and
netmask using slash notation; ex:
Enables remote SSH login “support” account or
localmode enable|/disable.
AAA.BBB.CCC.DD/X
disable} |
{localmode}
dns
50 Copyright© 2018, Juniper Networks, Inc.
Sets DNS (or enables DHCP for DNS) for the management interface by default if interface is unspecified.
Page 59
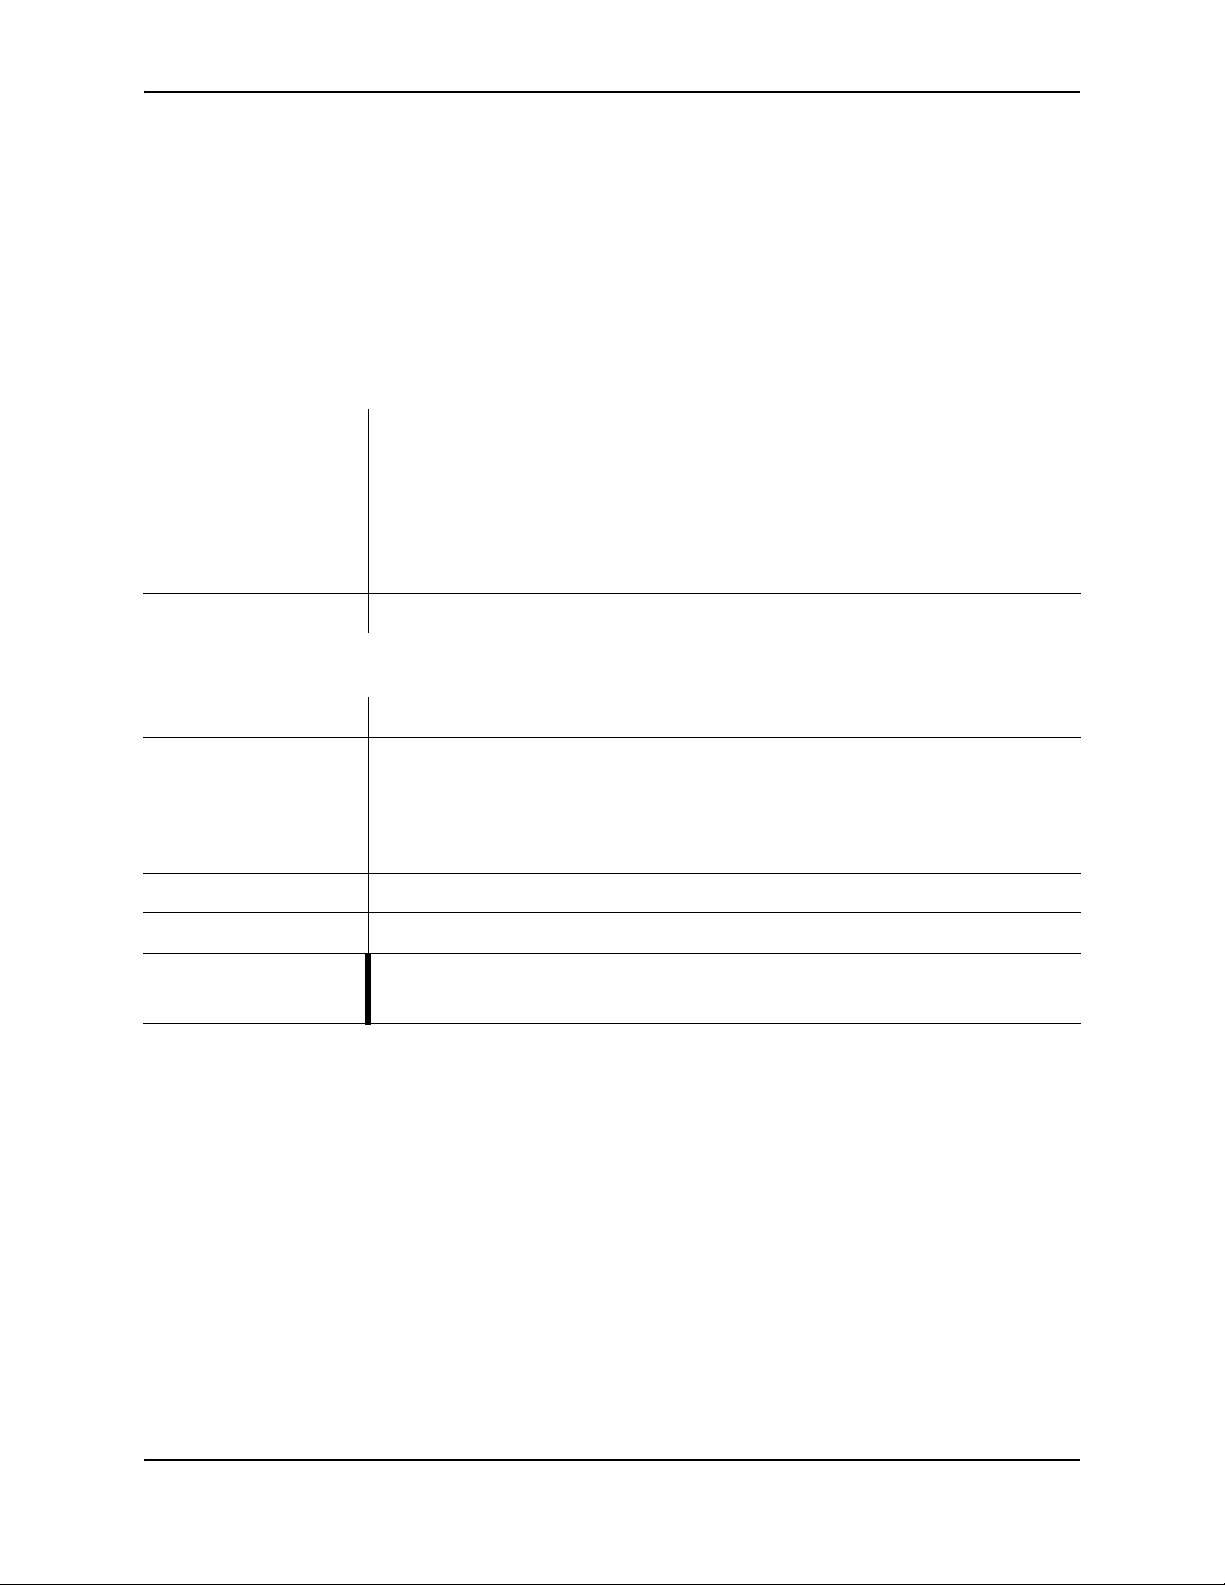
Table 3-18 set
firewall {all
<backup | flush>
| whitelist <add
| delete |
flush>}
CLI Command Reference Guide
Backs up or flushes (clears) all current iptables
for a firewall, or adds, deletes or flushes the
current iptables whitelist-specific settings for the
firewall.
The “add” option adds an IP address to the
iptables outbound whitelist.
# set firewall whitelist add
10.1.1.1
hostname string
ip interface
{management |
alternateexhaust} <dhcp |
address |
netmask |
gateway}
ntpserver
passphrase
string
password
proxy {config
<all|http> |
enable <on|off>
| remove
<all|http>}
timezone string
uipassword
Sets the system’s host name.
Sets the IP address, netmask, or default gateway,
or enables DHCP for the management or
alternate-exhaust interface.
Sets the Network Time Protocol (NTP) server.
Sets the device key password; enter a string.
Sets a new password for the CLI administrator.
Config, enable/disable, or remove “all” proxy configs,
or remove an HTTP-specific proxy server.
Tip: Config the proxy for “all” protocols first, and then
change HTTP proxy as needed.
Sets the timezone for the device.
Sets a new admin password for CM Web UI access.
Examples
The following example enables a proxy server.
JATP (server)# set proxy enable on
Copyright© 2018, Juniper Networks, Inc. 51
Page 60
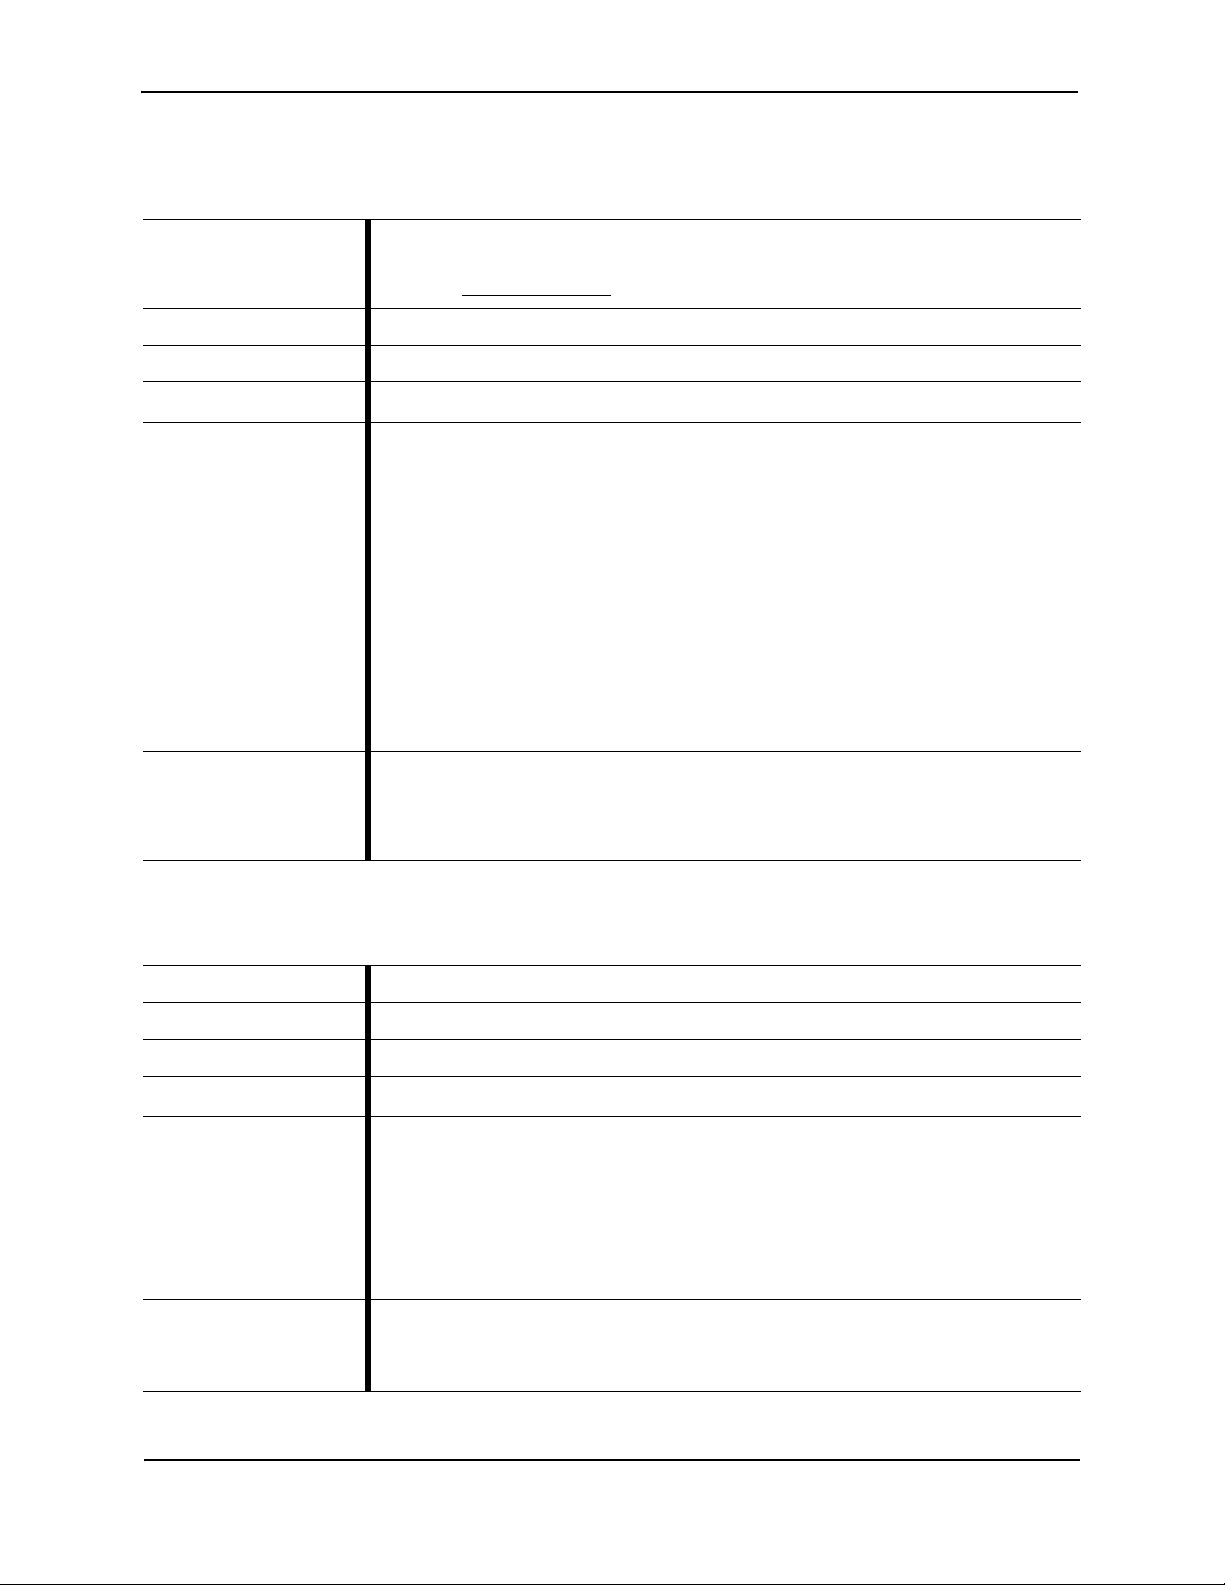
Juniper Advanced Threat Prevention Appliance
all
Sets logging for all Juniper ATP Appliance components.
default
Sets logging to the default parameters.
debug
Sets logging at the debug level.
info
Sets logging at the info level.
warning
Sets logging at the warning level.
error
Sets logging at the error level.
critical
Sets logging at the critical level.
all
Checks both basic settings and analysis pipelin
report
Shows report of last setupcheck.
basic
Checks basic configuration settings.
analysis
Checks the analysis pipeline.
set (diagnosis mode)
Table 3-19 set
Sets the logging levels for Juniper ATP Appliance components from diagnosis
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
mode.
See Also: set (server mode)
Syntax
Parameters
Example
setupcheck
Table 3-20 setupcheck
set logging all
The following example sets the default logging level for all Juniper ATP Appliance
components.
JATP(diagnosis)# set logging all
52 Copyright© 2018, Juniper Networks, Inc.
Description Checks and reports on basic configuration settings and analysis pipeline setup.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Example
setupcheck {all | report | basic | analysis}
The following example checks all basic configuration settings as well as the
analysis pipeline:
JATP (diagnosis) # setupcheck all
Page 61
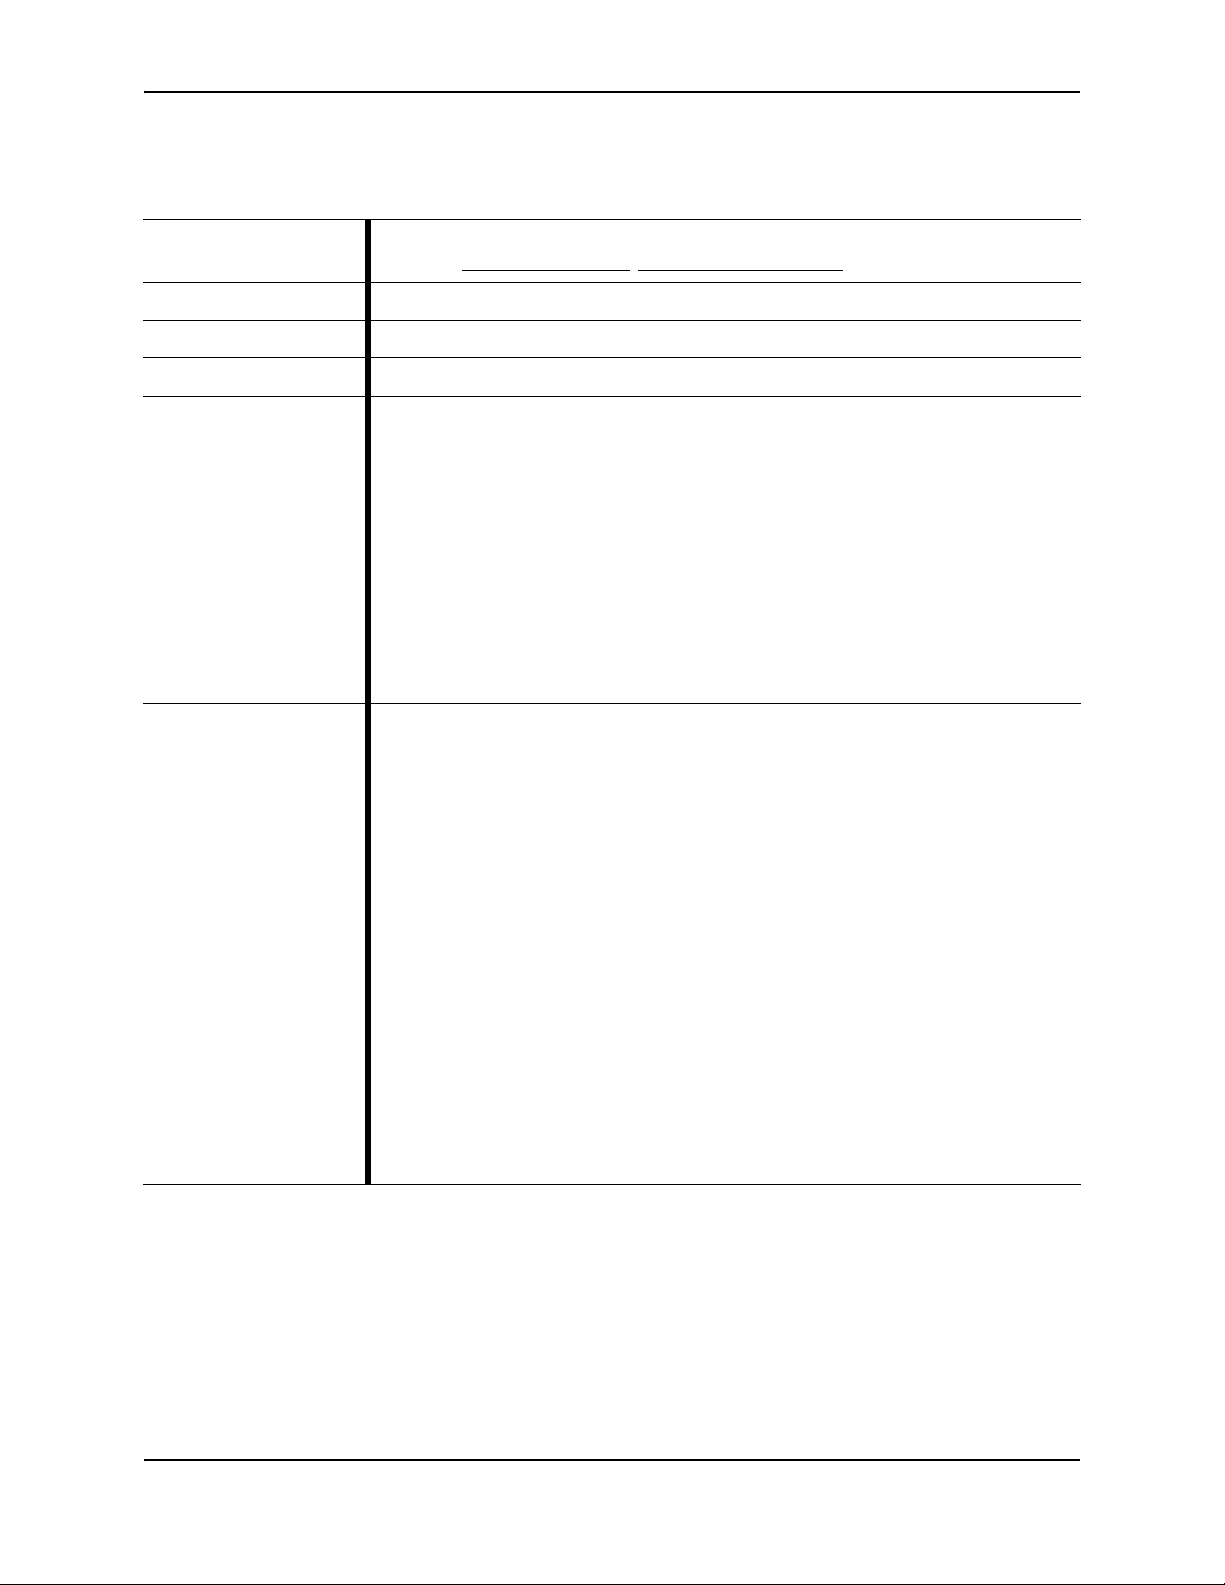
show (core mode)
images Displays guest image update and status information.
whitelist Displays the name, hit count and the time of last hit of a user
configured whitelist.
Note that when a whitelist rule is deleted, it will be removed
from the list. Updates to existing rule are not affected by the
presence of the rule in the output, but hit count could
increment. Further, more than one rule can be hit by a single
incident.
alternateexhaustinterface
Displays the status of the alternate exhaust interface eth2.
Table 3-21 show
CLI Command Reference Guide
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Core
Syntax
Parameters
Displays the guest image(s) status or whitelist statistics.
See Also: show (server mode)
; show (diagnostic mode)
show
The following example demonstrates the show images command usage:
JATP(core)# show images
The following example demonstrates the show whitelist command usage:
JATP(core)# show whitelist
JATP(core)# show whitelist
Rule Name Hit Count Local Time of Last Hit
Example
URI1 10 Wed Sep 2 18:16:55 2015
URI2 10 Wed Sep 2 18:16:55 2015
URI3 10 Wed Sep 2 18:16:55 2015
greatfilesarey 49 Wed Sep 2 18:20:00 2015
The following example shows how to get the alternate-exhaust interface (eth2)
status:
JATP(core)# show alternate-exhaust interface
Copyright© 2018, Juniper Networks, Inc. 53
Page 62
Juniper Advanced Threat Prevention Appliance
device
{collectorstatus | |
corestatus |
slavecorestatus}
Display connected device statistics for Traffic Collector,
CoreCM, or Mac Mini Detection Engine Secondary “slave
core.”
protocol {web |
email}
Displays the session counts for network web or email
protocols.
objects Displays the current number of file objects.
logging Displays the currently-configured logging level.
See Also: set (diagnosis mode) logging
log error traceback Displays only the tracebacks (if any) generated by
Juniper ATP Appliance OS process error logs. A
traceback is a stack of functions that were executing
when an error condition was encountered.
log error last
<integer: number of
lines to display>
Displays n [1-1000] lines of the contents of the
common log file.
Example: show log error last 12
show (diagnosis mode)
Description
Product(s) CLI
Mode(s)
Syntax
Parameters
Displays diagnostics information.
See Also: show (server mode)
All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
diagnosis
show
The following example displays the connected Traffic Collector status.
JATP(diagnosis)# show device collectorstatus
<cr>
JATP (diagnosis)# show device collectorstatus
WEB_COLLECTOR
=========================================================
IP : 10.2.9.68
Example
Enabled : True
Last Seen : 2014-07-25 15:13:17.967000-07:00
Install Date : 2014-06-25 19:03:38-07:00
=========================================================
IP : 10.2.20.3
Enabled : True
54 Copyright© 2018, Juniper Networks, Inc.
Last Seen : 2014-07-28 11:07:42.046000-07:00
Install Date : 2013-11-14 09:25:39-08:00
Page 63
CLI Command Reference Guide
show (server mode)
Table 3-22 show
Description Display configurations and status information.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server, See Also: show (diagnosis mode)
Syntax
Parameters
(See tables below)
autoupdate
cli timeout
clock
cm
controller
support
description
devicekey
devicetype
show
Show the automatic update setting.
Show the CLI timeout setting.
Show the current date and time.
Show the Central Manager IP address.
Show the driver state for interfaces.
Show the remote SSH login support status.
Show the server or system description.
Show the device key.
Show the device type.
dns
eula
firewall [all <|
whitelist]
hostname
interface [management |
monitoring | alternateexhaust]
See Also:
show controller
ip
Show the DNS servers settings.
Show the End User License Agreement.
Show the firewall configuration settings.
Show the system’s host name.
Show information about the management
(administrative) network interface eth0, or the
monitoring interface (eth1), or the
alternate-exhaust interface (eth2).
Show the IP address of the management
(administrative) interface eth0.
Results may show both private and public IP
addresses if the AWS vCore has a public IP.
Copyright© 2018, Juniper Networks, Inc. 55
Page 64
Juniper Advanced Threat Prevention Appliance
name
ntpserver
proxy
See also show (collector mode)
for show proxy inside/outside
data path
stats [cpuload | disk |
memory]
system-alert
Show the server name.
Show the Network Time Protocol (NTP) server
settings.
Shows the proxy configuration for the management network.
Show system statistics:
cpuload shows average CPU load in the
system for running processes in the last 1, 5 and
15 min intervals.
disk shows the disk space usage in the system.
memory shows the system memory usage.
show stats cpuload (0.06,0.13,0.13)
Shows the current set system-alert settings.
Show the current timezone; example:
set timezone US/Pacific
TIP:
set timezone <tab> shows options.
timezone {US/Eastern |
US/Central | US/
Mountain
uptime
uuid
version
Show how long the system has been running.
Show the system UUID (universally unique ID).
Show Juniper ATP Appliance software and content
security
versions.
56 Copyright© 2018, Juniper Networks, Inc.
Page 65
Example
CLI Command Reference Guide
The following example displays information about the CoreCM server device type:
CoreCM(server)# show devicetype
Device type: cm, core
The following example requests data about the alternate-exhaust interface (eth2):
CoreCM(server)# show interface alternate-exhaust
The following example shows details about the Collector’s monitoring interface
(eth1):
CoreCM(server)# show interface monitoring
Interface: monitoring (eth1) Enabled: Yes Link: Yes
IP Address: unknown Mask: unknown MTU: 1500
MAC Address: 90:d6:1f:22:70:g6 Speed: 1000Mb/s Duplex:
Full
Auto-negotiation: Yes Medium: Copper
RX packets: 1869032424 Bytes: 1716560257902 Errors: 0
Overruns: 0
TX packets: 409287 Bytes: 44607401 Errors: 0 Overruns: 0
Traffic rate for the last 5 seconds/1 minute/5 minutes
RX bits/sec: 108616/160176/442736
RX packets/sec: 44/46/91
TX bits/sec: 0/112/128
TX packets/sec: 0/0/0
Copyright© 2018, Juniper Networks, Inc. 57
Page 66
Juniper Advanced Threat Prevention Appliance
-h unsigned
integer
Specifies the number of hops
string
Names the remote system to be traced.
<String_URI>
Specifies the software packages to copy .from a remo
location for upgrading via the Core.
shutdown
Table 3-23 shutdown
Description Shuts down the Juniper ATP Appliance server.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters None
Example
shutdown
The following example performs a shutdown of the current device.
JATP# shutdown
traceroute
Table 3-24 traceroute
Description Displays the route packets trace to a host name or an IP address.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
traceroute
The following example performs a traceroute of the named device.
JATP# traceroute -h 2 MacMininOSX-Engine
upgrade
Table 3-25 upgrade
Description
Product(s) CLI All-in-One | Core CM
Mode(s) cm
Syntax
Parameters
58 Copyright© 2018, Juniper Networks, Inc.
Upgrade Juniper ATP Appliance software for the Core/CM device or vCore, and all
connected physical or virtual devices.
upgrade <URI as user@hostname:path>
Page 67
Table 3-25 upgrade
built-in Updates the guest-image on the detection Engine.
Example
updateimage
Table 3-26 updateimage
Description
CLI Command Reference Guide
The following example copies Juniper ATP Appliance software to the Core from a
remote location defined by the path provided.
CoreCM(cm)# upgrade [email protected]:some/remote/
directory
Update or correct the guest-image OS profile used by the detection and analysis
behavioral engine.
The updateimage command will update the guest images from a USB drive
attached to the Juniper ATP Appliance.
Product(s) CLI All-in-One | Core-CM | Mac Mini OS X Detection Engine
Mode(s) Core
Syntax
Parameters
updateimage
The following example performs a built-in profile update for the Core detection
engine.
JATP (core)# updateimage built-in
Installing image SC-XP-20140617.img...
Previous version of SC-XP-20140617.img exists.
Example
Checking integrity...
Image SC-XP-20140617.img is already installed
Installing image SC-W7-20140521.img...
Previous version of SC-W7-20140521.img exists.
Checking integrity...
Image SC-W7-20140521.img is already installed
wizard
Table 3-27 wizard
Enters the Configuration Wizard. For Configuration Wizard commands and
Description
Product(s) CLI All-in-One | Core/CM | Collector | Mac Mini Mac OS X
Mode(s) Basic
response, see “Configuration Wizard for the CoreCM Server” in the next section to
follow command prompts and recommended responses.
Copyright© 2018, Juniper Networks, Inc. 59
Page 68
Juniper Advanced Threat Prevention Appliance
Table 3-27 wizard
Syntax
Parameters None
Example
wizard
The following command starts the configuration wizard.
hostname # wizard
Configuration Wizard for the CoreCM Server
NOTE Enter CTRL-C to exit the Configuration Wizard at any time. If you exit without completing the
configuration, you will be prompted again whether to run the Configuration Wizard.
You may also rerun the Configuration Wizard at any time with the CLI command wizard.
Configuration Wizard Prompts Customer Response Actions
Use DHCP to obtain the IP address and DNS
server address for the administrative interface
(Yes/No)?
Note: Only if your DHCP response is no,enter
the following information when prompted:
a. IP address (no CIDR format)
b. Netmask
c. Enter a gateway IP address for this
management (administrative) interface:
d. Enter primary DNS server IP address.
e. Do you have a secondary DNS Server
(Yes/No).
f. Do you want to enter the search
domains?
g. Enter the search domain (separate
multiple search domains by space):
Restart the administrative interface (Yes/No)?
We strongly discourage the use of DHCP
addressing because it changes dynamically. A
static IP address is preferred.
Recommended: Respond with no:
a. Enter an IP address
b. Enter a netmask using the form
255.255.255.0.
c. Enter a gateway IP address.
d. Enter the DNS server IP address
e. If yes, enter the IP address of the secondary
DNS server.
f. Enter yes if you want DNS lookups to use a
specific domain.
g. Enter search domain(s) separated by spaces;
for example: example.com lan.com dom2.com
Enter yes to restart with the new configuration
settings applied.
60 Copyright© 2018, Juniper Networks, Inc.
Page 69
CLI Command Reference Guide
Enter a valid hostname. Type a hostname when prompted; do not
include the domain; for example: Juniper ATP
Appliance1
[OPTIONAL]
If the system detects a Secondary Core with an
eth3 port, then the alternate CnC exhaust
option is displayed:
Use alternate-exhaust for the analysis engine
exhaust traffic (Yes/No)?
Enter IP address for the alternate-exhaust
(eth2) interface:
Enter netmask for the alternate-exhaust (eth2)
interface: (example: 255.255.0.0)
Enter gateway IP Address for the alternateexhaust (eth2) interface: (example:10.6.0.1)
Enter primary DNS server IP Address for the
alternate-exhaust (eth2) interface: (example:
8.8.8.8)
Do you have a secondary DNS server for the
alternate-exhaust (eth2) interface?
Do you want to enter the search domains for
the alternate-exhaust (eth2) interface?
Note: A complete network interface restart can
take more than 60 seconds
Regenerate the SSL self-signed certificate
(Yes/No)?
Refer to “Configuring an Alternate Analysis
Engine Interface” in the Juniper ATP Appliance
Operator’s Guide for more information.
Enter yes to configure an alternate eth2
interface.
Enter the IP address for the eth2 interface.
Enter the eth2 netmask.
Enter the gateway IP address.
Enter the primary DNS server IP Address for the
alternate-exhaust (eth2) interface.
Enter yes or no to confirm or deny an eth2
secondary DNS server.
Enter yes or no to indicate whether you want to
enter search domain.
Enter
yes to create a new SSL certificate for
the Juniper ATP Appliance Server Web UI.
Enter the following server attributes:
Central Manager (CM) IP Address:
Device Name: (must be unique)
Device Description
Device Key PassPhrase
NOTE: Remember this passphrase and use it
for all distributed devices.
Copyright© 2018, Juniper Networks, Inc. 61
If you decline the self-signed certificate by
entering no, be prepared to install a certificate
authority (CA) certificate.
Is this a Central Manager device?:
Enter Yes; the system will auto-set IP 127.0.0.1
as the All-in-One IP address.
Enter a connected Juniper ATP Appliance
Collector Device Name; this identifies the
Collector in the Web UI.
Enter a device Description
Enter a user-defined PassPhrase to be used to
authenticate the Core to the Central Manager.
Page 70
Juniper Advanced Threat Prevention Appliance
62 Copyright© 2018, Juniper Networks, Inc.
Page 71
This chapter describes the CLI commands available for the Mac Mini Mac OS X “Secondary Core” detection
CHAPTER 4
Mac OS X Engine CLI Commands
engine device. There is no Collector Mode on this device.
NOTE You must enclose non-alphabet characters in double quotes in CLI commands.
Basic Mode Commands
Use general system commands to configure the appliance, view appliance history, enter other CLI modes, obtain
help with CLI syntax, and to exit the CLI session.
The general commands are:
• core on page 66
• diagnosis on page 66
• exit on page 67
• help on page 68
• history on page 69
• server on page 72
• wizard on page 83
Refer to the respective chapters in this guide to review Collector Mode, Diagnosis Mode and Server Mode
commands per device-- All-in-One, Mac OS X Engine, Traffic Collector and CoreCM.
Core Mode Commands
• exit on page 67
• help on page 68
• history on page 69
• show (core mode) on page 77
• updateimage on page 81
Copyright© 2018, Juniper Networks, Inc. 63
Page 72
Juniper Advanced Threat Prevention Appliance
Server Mode Commands
• exit on page 67
• help on page 68
• history on page 69
• ifrestart on page 69
• ping on page 70
• reboot on page 70
• restart on page 70
• restore on page 72
• server on page 72
• set (server mode) on page 74
• show (server mode) on page 79
• shutdown on page 81
• traceroute on page 81
Diagnosis Mode Commands
• capture-start on page 65
• copy on page 65
• exit on page 67
• gssreport on page 67
• help on page 68
• history on page 69
• set (diagnosis mode) on page 76
• setupcheck on page 77
• show (diagnosis mode) on page 78
64 Copyright© 2018, Juniper Networks, Inc.
Page 73
CLI Command Reference Guide
Mac OS X Detection Engine CLI Commands
capture-start
Table 4-1 capture-start
Starts packet capture as a means for diagnosing and debugging network traffic and
Description
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Diagnosis
obtaining stats (not part of the Collector traffic capture engine).
See Also: diagnosis
[mode]; copy
Syntax
Parameters <IP address> <interface_name>
Sub-Commands None
capture-start
The following example starts a packet capture process on interface eth1 for a
Juniper ATP Appliance with IP address 8.8.8.8:
hostname # diagnosis
Example
copy
Table 4-2 copy
Description
Product(s) CLI
hostname (diagnosis)# capture-start 8.8.8.8 eth1
NOTE Note: Address 8.8.8.8 need not be a Juniper ATP Appliance. It is just
a host that the capture filters on.
Uses Secure Copy (SCP) to scp to copy and transfer packet capture or traceback
(crash) data to a remote location, providing the same authentication and level of
security as an SSH transfer.
See Also: diagnosis
All-in-One | Collector | Core | Mac OS X Detection Engine
[mode]; capture-start
Mode(s) Diagnosis
copy capture <scp source_file_name
Syntax
username@destination_host:destination_folder> | traceback
all <string URI as user@hostname:path>
copy capture <scp remote filename_location>
Parameters
copy traceback all <path string>
copy traceback <tab>
Sub-Commands None
The following example copies the file "captureEth1.txt" from the local host to a
remote host:
Example
hostname (diagnosis)# copy capture scp captureEth1.txt
[email protected]:/some/remote/directory
[tab displays all available crash filenames]
Copyright© 2018, Juniper Networks, Inc. 65
Page 74
Juniper Advanced Threat Prevention Appliance
core
Table 4-3 core
Enters core mode.
Description
See Also: basic [mode];
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Basic
Syntax
Parameters None
Sub-Commands
Example
core
exit, help, history, show, updateimage
The following command example enters core configuration mode:
hostname # core
hostname (core)#
diagnosis
Table 4-4 diagnosis
Enters the Diagnosis configuration and status check mode.
Description
See Also: collector [mode], server [mode]
Product(s) CLI All-in-One | Collector | Core | Mac OS X Detection Engine
Mode(s) Basic
Syntax
Parameters None
diagnosis
capture-start; copy; exit; gssreport; help; history; set
Sub-Commands
(server mode); setupcheck; show (diagnosis mode); show
(server mode)
The following example enters diagnosis configuration and status check mode:
Example
hostname # diagnosis
hostname (diagnosis)# ?
66 Copyright© 2018, Juniper Networks, Inc.
Page 75
CLI Command Reference Guide
exit
Table 4-5 exit
Description Ends the CLI session.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Server | Diagnosis
Syntax
Parameters None
Example
exit
The following example ends the CLI session.
JATP# (diagosis) exit
JATP#
gssreport
Table 4-6 gssreport
Use the gssreport command to submit reports to Juniper ATP Appliance Global
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Sub-Commands None
Security Services (GSS), and to display the status of the current GSS report.
See Also: gssreport
; diagnosis [mode]
gssreport status | submit
status - displays the status of the current GSS report.
submit - submits a report to Juniper ATP Appliance GSS.
Example
The following examples display the status of a GSS report submission:
hostname # diagnosis
hostname (diagnosis)# gssreport submit
Successfully started GSS report
hostname (diagnosis)# gssreport status
GSS is currently enabled
Last 5-minute GSS report at 2014-07-28 10:34:24.414322:
successfully submitted
Last hourly GSS report at 2014-07-28 10:34:24.468259:
successfully submitted
Last daily GSS report at 2014-07-28 10:34:28.225512:
successfully submitted
Copyright© 2018, Juniper Networks, Inc. 67
Page 76
Juniper Advanced Threat Prevention Appliance
help
Table 4-7 help
Description Displays information about the CLI help system.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Server | Diagnosis
Syntax
Parameters None
Example
help
The following example shows some of the output of the help command.
CONTEXT SENSITIVE HELP
[?] - Display context sensitive help. This is either a list of
possible command completions with summaries, or the full syntax
of the current command. A subsequent repeat of this key, when a
command has been resolved, will display a detailed reference.
AUTO-COMPLETION
The following keys both perform auto-completion for the current
command line. If the command prefix is not unique then the bell
will ring and a subsequent repeat of the key will display
possible completions.
[enter] - Auto-completes, syntax-checks then executes a command.
If there is a syntax error then offending part of the command
line will be highlighted and explained.
[tab] - Auto-completes
[space] - Auto-completes, or if the command is already resolved
inserts a space.
If “<cr>” is shown, that means that what you have entered so
far is a complete command, and you may press Enter (carriage
return) to execute it.
Use ? to learn command parameters and option:
JATP(server)# show f?
firewall Show the firewall configuration settings
interface
JATP(server)# show firewall?
all Show the current iptables settings
whitelist Show the iptables whitelist settings
show firewall whitelist?
<cr>
show firewall whitelist
68 Copyright© 2018, Juniper Networks, Inc.
Page 77
CLI Command Reference Guide
eth0
Restarts the management network administra
interface.
eth1
Restarts the monitoring network interface.
history
Table 4-8 history
Description Displays the current CLI session command line history.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Server | Diagnosis
Syntax
Parameters None
Example
history
The following examples returns command line history for the current CLI session.
JATP# history
ifrestart
Table 4-9 ifrestart
Description Restarts the interface driver and services using the interface.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
ifrestart eth0 | eth1
The following example restarts the eth0 interface for the management network.
JATPMAC (server) # ifrestart eth0
Copyright© 2018, Juniper Networks, Inc. 69
Page 78
Juniper Advanced Threat Prevention Appliance
-c count
Number of echo requests to send. By default, pings ar
continuously until you press Ctrl+C.
-h hops
Number of next hops between pings (default is 1).
string
IP address, hostname or interface name used to ping
device address.
ping
Table 4-10 ping
Sends ICMP (Internet Control Message Protocol) echo request packets to a
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
specified host name or IP address to verify that the destination is reachable over
the network.
Syntax
Parameters
Example
reboot
ping [-c count] [-h hops] [string]
The following example sends three echo requests to the device with the IP Address
10.10.10.1
<FireEye_name>#
PING 10.10.10.1 (10.10.10.1) 56(84) bytes of data.
64 bytes from 10.10.10.1: icmp_req=1 ttl=64 time=0.314 ms
64 bytes from 10.10.10.1: icmp_req=2 ttl=64 time=0.277 ms
64 bytes from v: icmp_req=3 ttl=64 time=0.274 ms
--- 10.10.10.1 ping statistics --3 packets transmitted, 3 received, 0% packet loss, time
bbbb1999ms
rtt min/avg/max/mdev = 0.274/0.288/0.314/0.022 ms
ping -c 3 10.10.10.1
Table 4-11 reboot
restart
Table 4-12 restart
70 Copyright© 2018, Juniper Networks, Inc.
Description Reboots the Juniper ATP Appliance.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters None
Example
Description Restarts Juniper ATP Appliance services.
reboot
The following example reboots the system.
hostname# reboot
Page 79
CLI Command Reference Guide
all
Restarts all Juniper ATP Appliance services.
database
Restarts the Database.
ntpserver
Restarts the NTP server.
sshserver
Restarts the SSH server.
Table 4-12 restart
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
restart [all | behaviorengine | cm | collector | core |
Syntax
Parameters
Example
correlationengine | database | ntpserver | sshserver |
staticengine | webserver]
The following example restarts the Central manager service.
JATP# restart cm
Copyright© 2018, Juniper Networks, Inc. 71
Page 80
Juniper Advanced Threat Prevention Appliance
support
Restores the default support password setting for SSH
remote login (set during initial installation per license).
See also (server)# set (server mode) support
firewall
{backup |
default}
Restores the firewall settings from either the previous
backup, or from the default factory settings.
hostname
Restores the system’s hostname to the factory default
hostname.
network
Restores the IP address and DNS settings to the
factory default settings.
WARNING: This command option removes the current
IP address and DNS settings, and reloads the default
values for these settings.
restore
Table 4-13 restore
Description Restores the system configuration to the factory default settings.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
NOTE: Whitelist rules
rely on normal service
shutdown to be backed
up.Powering off a VM
directly will lose the
whitelist state as rules
cannot be saved in that
case
Example
restore [support | firewall {backup | default} | hostname
| network]
The following example restores the system.
JATP# restore
This next example restores the SSH login “support” password to the default.
JATP# restore support password
Restore the default suppport password? (Yes/No)? yes
support password was restored successfully!
server
Table 4-14 server
Description Enters the server configuration mode.
Product(s) CLI All-in-One | Collector | Core/CM | Mac Mini Mac OS X
Mode(s) Basic
Syntax
Sub-Commands
72 Copyright© 2018, Juniper Networks, Inc.
server
exit; help; history; ifrestart; ping; reboot; restore; set
(server mode); show (server mode); traceroute; updateimage
Page 81
Table 4-14 server
CLI Command Reference Guide
The following example enters server configuration mode:
Example
hostname # server
hostname (server) # ?
Copyright© 2018, Juniper Networks, Inc. 73
Page 82
Juniper Advanced Threat Prevention Appliance
set (server mode)
Table 4-15 server mode
Description Configure the system settings.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server, See Also: set (diagnosis mode)
set [autoupdate {on | off} | cli timeout secs | clock | cm
address | support {on | off} | passphrase string | dns |
Syntax
firewall {all <backup | flush> | whitelist} | hostname
string | ip interface {management | alternate-exhaust}|
ntpserver | password | proxy {config | enabled | remove} |
timezone string | uipassword]
Parameters
(See table below)
autoupdate {on |
off}
cli timeout secs
clock
cm address
set support
{enable |
disable} |
{localmode}
passphrase
string
dns
firewall {all
<backup | flush>
| whitelist <add
| delete |
flush>}
NOTE: Whitelist rules
rely on normal service
shutdown for
backup.Powering off a
VM directly loses the
whitelist state as rules
cannot be saved in that
case.
Turn on or off the automatic product update feature.
Set CLI timeout period in seconds (0 = no timeout).
Sets the current date and time.
Sets the IP address of the Central Manager and
netmask using the slash notation; example:
AAA.BBB.CCC.DD/x
Enables remote SSH login “support” account or
localmode enable|/disable.
Sets the device key password; enter a string.
Sets the DNS servers (or enable DHCP for DNS)
for the management interface eth0.
Backs up or flushes (clears) all current iptables
for a firewall, or adds, deletes or flushes the
current iptables whitelist-specific settings for the
firewall.
The “add” option adds an IP address to the
iptables outbound whitelist.
# set firewall whitelist add
10.1.1.1
hostname string
74 Copyright© 2018, Juniper Networks, Inc.
Sets the system’s host name.
Page 83
Table 4-15 server mode
CLI Command Reference Guide
ip interface
{management |
alternateexhaust} <dhcp |
address |
netmask |
gateway}
ntpserver
password
proxy {config
<all|http> |
enabled <on|off>
| remove
<all|http>}
timezone {US/
Eastern | US/
Central | US/
Mountain
uipassword
Sets the IP address, netmask, or default gateway,
or enables DHCP for the management or
alternate-exhaust interface.
Sets the Network Time Protocol (NTP) server.
Sets a new password for the CLI administrator.
Config, enable/disable, or remove “all” proxy configs,
or remove an HTTP-specific proxy server.
Tip: Config the proxy for “all” protocols first, and then
change HTTP proxy as needed.
Show the current timezone; example:
set timezone US/Pacific
TIP: set timezone <tab> shows options.
Sets a new admin password for CM Web UI access.
Example
The following example sets an ip address for the device management interface
eth0.
JATP# set ip interface 10.1.1.1
Copyright© 2018, Juniper Networks, Inc. 75
Page 84
Juniper Advanced Threat Prevention Appliance
all
Sets logging for all Juniper ATP Appliance components.
default
Sets logging to the default parameters.
debug
Sets logging at the debug level.
info
Sets logging at the info level.
warning
Sets logging at the warning level.
error
Sets logging at the error level.
critical
Sets logging at the critical level.
set (diagnosis mode)
Table 4-16 set
Sets the logging levels for Juniper ATP Appliance components from diagnosis
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
mode.
See Also: set (server mode)
Syntax
Parameters
Example
set logging
The following example sets the default logging level for all Juniper ATP Appliance
components.
JATP(diagnosis)# set logging all
76 Copyright© 2018, Juniper Networks, Inc.
Page 85
CLI Command Reference Guide
all
Checks both basic settings and analysis pipelin
report
Shows report of last setupcheck.
basic
Checks basic configuration settings.
analysis
Checks the analysis pipeline.
images
Displays guest image update and status information.
whitelist
Displays the name, hit count and the time of last hit of a user
configured whitelist.
Note that when a whitelist rule is deleted, it will be removed
from the list. Updates to existing rule are not affected by the
presence of the rule in the output, but hit count could
increment. Further, more than one rule can be hit by a single
incident.
alternateexhaustinterface
Displays the status of the alternate exhaust interface eth2.
setupcheck
Table 4-17 setupcheck
Description Checks and reports on basic configuration settings and analysis pipeline setup.
Product(s) CLI All-in-One | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
Syntax
Parameters
Example
setupcheck {all | report | basic | analysis}
The following example checks all basic configuration settings as well as the
analysis pipeline:
JATP(diagnosis) # setupcheck all
show (core mode)
Table 4-18 show
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Core
Syntax
Displays the guest image(s) status.
See Also: show (server mode)
; show (diagnostic mode)
show
Parameters
Example
The following example demonstrates the show images command usage:
JATP(core)# show images
The following example shows how to get the alternate-exhaust interface (eth2)
status:
JATP(core)# show alternate-exhaust interface
Copyright© 2018, Juniper Networks, Inc. 77
Page 86
Juniper Advanced Threat Prevention Appliance
device
{collectorstatus
| | corestatus |
slavecorestatus}
Display connected device statistics for Traffic
Collector, CoreCM, or Mac Mini Detection Engine
“Secondary core.”
NOTE: Not available from the Mac Mini CLI.
protocol {web |
email}
Displays the session counts for network web or email
protocols. NOTE: Not available from the Mac Mini CLI.
objects
Displays the current number of file objects.
NOTE: Not available from the Mac Mini CLI.
logging
Displays the currently-configured logging level.
See Also: set (diagnosis mode) logging
log error
traceback
Displays only the tracebacks (if any) generated by
Juniper ATP Appliance OS process error logs. A traceback is
stack
of functions that were executing when an error
condition was encountered.
log error last
<integer: number
of lines to
Displays n [1-1000] lines of the contents of the
common log file.
show (diagnosis mode)
Table 4-19 show
Sets the logging levels for Juniper ATP Appliance components from diagnosis
Description
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) diagnosis
mode.
See Also: show (server mode)
Syntax
Parameters
Example
show
The following example displays the connected Traffic Collector status.
osx-1(server)# show devicetype
Device type: slave_core.
78 Copyright© 2018, Juniper Networks, Inc.
Page 87
CLI Command Reference Guide
show (server mode)
Table 4-20 show
Description Display configurations and status information.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server, See Also: show (diagnosis mode)
Syntax
Parameters
(See the columns
below)
autoupdate
cli
clock
cm
controller
support
description
devicekey
devicetype
dns
eula
firewall [all <|
whitelist]
show
Show the automatic update setting.
Show the CLI setting.
Show the current date and time.
Show the Central Manager IP address.
Show the driver state for interfaces.
Show support status.
Show the server or system description.
Show the device key.
Show the device type.
Show the DNS servers settings.
Show the End User License Agreement.
Show the firewall configuration settings.
hostname
interface
[management |
monitoring |
alternateexhaust]
ip
name
ntpserver
proxy
Show the system’s host name.
Show information about the management
(administrative) network interface eth0, or the
monitoring interface (eth1), or the
alternate-exhaust interface (eth2).
See Also:
Show the IP address of the management (administrative)
interface eth0.
Show the server name.
Show the Network Time Protocol (NTP) server settings.
Show current proxy configuration.
show controller
Copyright© 2018, Juniper Networks, Inc. 79
Page 88
Juniper Advanced Threat Prevention Appliance
Table 4-20 show
stats [cpuload |
disk | memory]
timezone
upgrade
uuid
uptime
version
Example
Show system statistics:
• cpuload shows the average CPU load in the system for running processes in the
last 1, 5 and 15 minute intervals.
• disk shows the disk space usage in the system.
• memory shows the system memory usage.
Show the current timezone.
Show the last manual upgrade-related information.
Show the system UUID (universally unique ID).
Show how long the system has been running.
Show Juniper ATP Appliance software and content security versions.
The following example displays information about the MacOSX cpuload statistics:
MacOSX (server)# # show stats cpuload
(0.06, 0.13, 0.13)
The following example requests details for the Collector’s monitoring interface
(eth1):
MacOSX(server)# show interface monitoring
80 Copyright© 2018, Juniper Networks, Inc.
Page 89
CLI Command Reference Guide
-h unsigned
integer
Specifies the number of hops
string
Names the remote system to be traced.
shutdown
Table 4-21 shutdown
Description Shuts down the Juniper ATP Appliance server.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters None
Example
shutdown
The following example performs a shutdown of the current device.
JATP# shutdown
traceroute
Table 4-22 traceroute
Description Displays the route packets trace to a host name or an IP address.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Server
Syntax
Parameters
Example
traceroute
The following example performs a traceroute of the named device.
MacOSX1# traceroute -h 2 MacMininOSX2-Engine
updateimage
Description
Product(s) CLI Mac Mini OS X Detection Engine
Mode(s) Core
Syntax
Update or correct the guest-image OS profile used by the MAC OS X detection and
analysis behavioral engine.
The updateimage command will update the guest images from a USB drive
attached to the Juniper ATP Appliance.
updateimage
Copyright© 2018, Juniper Networks, Inc. 81
Page 90
Juniper Advanced Threat Prevention Appliance
built-in
Updates the guest-image on the Mac OSX Detection
“Secondary core.”.
Parameters
The following example performs a built-in Mac OS X profile update for the Mac
Mini-based Secondary core detection engine.
MAC2(core)# updateimage built-in
Installing image SC-OSX-20131003.img...
Previous version of SC-OSX-20131003.img exists. Checking
integrity...
Latest Image SC-OSX-20131003.img is already installed
Example
Installing image SC-XP-20140617.img...
Previous version of SC-XP-20140617.img exists. Checking
integrity...
Image SC-XP-20140617.img is already installed
Installing image SC-W7-20140521.img...
Previous version of SC-W7-20140521.img exists. Checking
integrity...
Image SC-W7-20140521.img is already installed
82 Copyright© 2018, Juniper Networks, Inc.
Page 91
upgrade
built-in Updates the guest-image on the Mac OSX Detection
“secondary core.”.
Table 4-23 upgrade
Upgrade a configured Juniper ATP Appliance Mac OSX Mac Mini device. If the Mac
Mini has already been upgraded to Ubuntu 14.04, this upgrade command will not be
visible at the CLI because it will not be needed.
Please note that this command will only show up for existing customers that have
Description
Product(s) CLI Mac Mini OS X Detection Engine
Mode(s) Core
Mac Mini devices configured as Juniper ATP Appliance Mac OSX detection engine
Secondary Cores (running Ubuntu 13.10). For new customers running Juniper ATP
Appliance Release 3.2.5, each Mac Mini device is shipped with the new Ubuntu
14.04 version already installed, so in this case, the upgrade command will again not
be available from the Juniper ATP Appliance Mac OSX Engine CLI.
CLI Command Reference Guide
Syntax
Parameters
Example
upgrade
The following example performs a built-in Mac OS X profile update for the Mac
Mini-based Secondary core detection engine.
MAC2(core)# upgrade
wizard
Table 4-24 wizard
Enters the Configuration Wizard. For Configuration Wizard commands and
Description
Product(s) CLI All-in-One | Core/CM | Collector | Mac Mini Mac OS X
Mode(s) Basic
Syntax
Parameters None
response, refer to “Configuration Wizard Command Prompt Responses” in the next
section to see command prompts and recommended responses.
wizard
The following command starts the configuration wizard.
Example
hostname # wizard
Copyright© 2018, Juniper Networks, Inc. 83
Page 92
Juniper Advanced Threat Prevention Appliance
Configuration Wizard Command Prompt Responses
Configuration Wizard Prompts Customer Response from the Mac Mini
Use DHCP to obtain the IP address and DNS server
address for the administrative interface (Yes/No)?
Note: Only if your DHCP response is no,enter the
following information when prompted:
a. IP address (no CIDR format)
b. Netmask
c. Enter a gateway IP address for this
management (administrative) interface:
d. Enter primary DNS server IP address.
e. Do you have a secondary DNS Server (Yes/
No).
f. Do you want to enter the search domains?
g. Enter the search domain (separate multiple
search domains by space):
Restart the administrative interface (Yes/No)?
We strongly discourage the use of DHCP addressing
because it changes dynamically. A static IP address
is preferred.
Recommended: Respond with no:
a. Enter an IP address
b. Enter a netmask using the form 255.255.255.0.
c. Enter a gateway IP address.
d. Enter the DNS server IP address
e. If yes, enter the IP address of the secondary DNS
server.
f. Enter yes if you want DNS lookups to use a specific
domain.
g. Enter search domain(s) separated by spaces; for
example: example.com lan.com dom2.com
Enter yes to restart with the new configuration
settings applied.
Enter a valid hostname. Type a hostname when prompted; do not include
the domain; for example: juniperatp1
84 Copyright© 2018, Juniper Networks, Inc.
Page 93
CLI Command Reference Guide
Configuration Wizard Prompts Customer Response from the Mac Mini
[OPTIONAL]
If the system detects a Secondary Core with an eth2
port, then the alternate CnC exhaust option is
displayed:
Use alternate-exhaust for the analysis engine
exhaust traffic (Yes/No)?
Enter IP address for the alternate-exhaust (eth2)
interface:
Enter netmask for the alternate-exhaust (eth2)
interface: (example: 255.255.0.0)
Enter gateway IP Address for the alternate-exhaust
(eth2) interface: (example:10.6.0.1)
Enter primary DNS server IP Address for the
alternate-exhaust (eth2) interface: (example:
8.8.8.8)
Do you have a secondary DNS server for the
alternate-exhaust (eth2) interface?
Do you want to enter the search domains for the
alternate-exhaust (eth2) interface?
Note: A complete network interface restart can take
more than 60 seconds
Regenerate the SSL self-signed certificate (Yes/
No)?
Refer to “Configuring an Alternate Analysis Engine
Interface” in the Juniper ATP Appliance Operator’s
Guide for more information.
Enter yes to configure an alternate eth2 interface.
Enter the IP address for the eth2 interface.
Enter the eth2 netmask.
Enter the gateway IP address.
Enter the primary DNS server IP Address for the
alternate-exhaust (eth2) interface.
Enter yes or no to confirm or deny an eth2 secondary
DNS server.
Enter yes or no to indicate whether you want to enter
search domain.
Enter yes to create a new SSL certificate for the
Juniper ATP Appliance Server Web UI.
Enter the following server attributes:
Central Manager (CM) IP Address:
Device Name: (must be unique)
Device Description
Device Key PassPhrase
NOTE: Remember this passphrase and use it for all
distributed devices!
If you decline the self-signed certificate by entering
no, be prepared to install a certificate authority (CA)
certificate.
Required:Enter the IP address of the Juniper ATP
Appliance Server Core/CM or All-in-One.
Enter a Juniper ATP Appliance Mac Mini or Core/CM
Device Name; this identifies the Mac OS X or Core
Engine in the Web UI.
Enter a device Description
Enter the same PassPhrase used to authenticate the
Core or Mac Mini to the Central Manager.
Copyright© 2018, Juniper Networks, Inc. 85
Page 94
Juniper Advanced Threat Prevention Appliance
86 Copyright© 2018, Juniper Networks, Inc.
Page 95
This chapter describes the commands specific to the Juniper ATP Appliance Collector CLI. The available
CHAPTER 5
Traffic Collector CLI Commands
commands are as follows:
Basic Mode Commands
• collector on page 89
• diagnosis on page 90
• exit on page 91
• help on page 92
• history on page 93
• server on page 97
• wizard on page 108
Collector Mode Commands
• exit on page 91
• help on page 92
• history on page 93
• set honeypot (collector mode) on page 98
• set proxy (collector mode) on page 97
• set proxy (collector mode) on page 97
• set protocols (collector mode) on page 99
• set traffic-filter (collector mode) on page 102
• show (collector mode) on page 104
Copyright© 2018, Juniper Networks, Inc. 87
Page 96
Juniper Advanced Threat Prevention Appliance
Diagnosis Mode Commands
• capture-start on page 89
• copy on page 90
• exit on page 91
• gssreport on page 91
• help on page 92
• history on page 93
• set (diagnosis mode) on page 99
• setupcheck on page 103
• show (diagnosis mode) on page 105
Server Mode Commands
• exit on page 91
• help on page 92
• history on page 93
• ifrestart on page 93
• ping on page 94
• reboot on page 94
• restart on page 94
• restore on page 96
• set (server mode) on page 100
• show (server mode) on page 106
• shutdown on page 108
• traceroute on page 108
88 Copyright© 2018, Juniper Networks, Inc.
Page 97
Traffic Collector CLI Commands
capture-start
Table 5-1 capture-start
Starts packet capture as a means for diagnosing and debugging network traffic and
Description
Product(s) CLI All-in-One | Collector
Mode(s) Diagnosis
obtaining stats (not part of the Collector traffic capture engine).
See Also: diagnosis
CLI Command Reference Guide
[mode]; collector [mode]; copy
Syntax
Parameters
Sub-Commands None
capture-start
<IP address> <interface_name>
The following example starts a packet capture process on interface eth1 for a
Traffic Collector with IP address 8.8.8.8:
hostname # diagnosis
Example
collector
Table 5-2 collector
Description
Product(s) CLI All-in-One | Collector
Mode(s) Basic
hostname (diagnosis)# capture-start 8.8.8.8 eth1
NOTE Note: Address 8.8.8.8 need not be a Juniper ATP Appliance. It is just
a host that the capture filters on.
Enters the Collector configuration mode.
See Also: server
[mode]
Syntax
Parameters None
Sub-Commands
Example
collector
exit; help; history; set proxy (collector mode); show
(collector mode)
The following example enters collector configuration mode:
hostname # collector
hostname (collector)# ?
Copyright© 2018, Juniper Networks, Inc. 89
Page 98
Juniper Advanced Threat Prevention Appliance
copy
Table 5-3 copy
Uses Secure Copy (SCP) to scp to copy and transfer packet capture or traceback
(crash) data to a remote location, providing the same authentication and level of
security as an SSH transfer.
Description
The copy traceback command, upon Customer Support's request, copies
the traceback files out of the box to a remote location.
See Also: diagnosis [mode]; capture-start
Product(s) CLI All-in-One | Collector | Core-CM | Mac OSX Engine
Mode(s) Diagnosis
copy capture <scp source_file_name
Syntax
username@destination_host:destination_folder> | traceback
ALL <string URI as user@hostname:path>
copy capture <scp remote filename_location>
Parameters
copy traceback all <path string>
copy traceback <tab>
[tab displays all available crash filenames]
Sub-Commands None
The following example copies the file "captureEth1.txt" from the local host to a
remote host:
Example
hostname (diagnosis)# copy capture scp captureEth1.txt
[email protected]:/some/remote/directory
diagnosis
Table 5-4 diagnosis
Enters the Diagnosis configuration and status check mode.
Description
See Also: collector [mode], server [mode]
Product(s) CLI
Mode(s) Basic
Syntax
Parameters None
All-in-One | Collector | Mac OS X Detection Engine
diagnosis
capture-start; copy; exit; gssreport; help; history; set
Sub-Commands
(server mode); setupcheck; show (diagnosis mode); show
(server mode)
The following example enters diagnosis configuration and status check mode:
Example
hostname # diagnosis
hostname (diagnosis)# ?
90 Copyright© 2018, Juniper Networks, Inc.
Page 99
CLI Command Reference Guide
exit
Table 5-5 exit
Description Ends the CLI session.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Server | Collector | Diagnosis
Syntax
Parameters None
Example
exit
The following example ends the CLI session.
JATP# (diagosis) exit
JATP#
gssreport
Table 5-6 gssreport
Use the gssreport command to submit reports to Global Security Services (GSS),
Description
Product(s) CLI
Mode(s) diagnosis
Syntax
Parameters
and to display the status of the current GSS report.
See Also: gssreport; diagnosis [mode]
All-in-One | Collector | Mac OS X Detection Engine
gssreport status | submit
status - displays the status of the current GSS report.
submit - submits a report to Juniper ATP Appliance GSS.
Sub-Commands None
The following examples display the status of a GSS report submission:
hostname # diagnosis
hostname (diagnosis)# gssreport submit
Successfully started GSS report
Example
hostname (diagnosis)# gssreport status
GSS is currently enabled
Last 5-minute GSS report at 2014-07-28 10:34:24.414322:
successfully submitted
Last hourly GSS report at 2014-07-28 10:34:24.468259:
successfully submitted
Last daily GSS report at 2014-07-28 10:34:28.225512:
successfully submitted
Copyright© 2018, Juniper Networks, Inc. 91
Page 100
Juniper Advanced Threat Prevention Appliance
help
Table 5-7 help
Description Displays information about the CLI help system.
Product(s) CLI All-in-One | Collector | Core CM | Mac Mini OS X Detection Engine
Mode(s) Basic | Server | Collector | Diagnosis
Syntax
Parameters None
help
The following example shows some of the output of the help command.
CONTEXT SENSITIVE HELP
[?] - Display context sensitive help. This is either a list of
possible command completions with summaries, or the full syntax
of the current command. A subsequent repeat of this key, when a
command has been resolved, will display a detailed reference.
AUTO-COMPLETION
The following keys both perform auto-completion for the current
command line. If the command prefix is not unique then the bell
will ring and a subsequent repeat of the key will display
possible completions.
[enter] - Auto-completes, syntax-checks then executes a command.
If there is a syntax error then offending part of the command
line will be highlighted and explained.
[tab] - Auto-completes
Example
[space] - Auto-completes, or if the command is already resolved
inserts a space.
If “<cr>” is shown, that means that what you have entered so
far is a complete command, and you may press Enter (carriage
return) to execute it.
Use ? to learn command parameters and option:
JATP (server)# show f?
firewall Show the firewall configuration settings
interface
JATP (server)# show firewall?
all Show the current iptables settings
whitelist Show the iptables whitelist settings
show firewall whitelist?
<cr>
show firewall whitelist
92 Copyright© 2018, Juniper Networks, Inc.
 Loading...