

Page 1

ADMINISTRATION
GUIDE
Cisco 300 Series Managed Switches Administration Guide
Page 2

2
Cisco and the Cisco logo are trademarks or registered trademarks of Cisco and/or its affiliates in the U.S. and other countries. To view a list of Cisco
trademarks, go to this URL: www.cisco.com/go/trademarks. Third-party trademarks mentioned are the property of their respective owners. The use
of the word partner does not imply a partnership relationship between Cisco and any other company. (1110R)
Cisco 300 Series Managed Switches Administration Guide 2
Page 3

Contents
Chapter 2: Getting Started 10
Starting the Web-based Configuration Utility 10
Quick Start Device Configuration 14
Interface Naming Conventions 14
Window Navigation 16
Chapter 3: Status and Statistics 20
System Summary 20
Ethernet Interfaces 20
Etherlike Statistics 22
GVRP Statistics 23
802.1X EAP Statistics 24
ACL Statistics 25
TCAM Utilization 25
Health 26
RMON 26
View Log 33
Chapter 4: Administration: System Log 34
Setting System Log Settings 34
Setting Remote Logging Settings 36
Viewing Memory Logs 37
Chapter 5: Administration: File Management 39
System Files 39
Upgrade/Backup Firmware/Language 42
Active Image 45
Download/Backup Configuration/Log 46
Configuration Files Properties 50
Copy/Save Configuration 51
Cisco 300 Series Managed Switches Administration Guide 1
Page 4

Contents
Auto Configuration/Image Update via DHCP 52
61
Chapter 6: Administration 62
Device Models 63
System Settings 65
Console Settings (Autobaud Rate Support) 68
Management Interface 68
User Accounts 68
Defining Idle Session Timeout 69
Time Settings 69
System Log 69
File Management 69
Rebooting the Device 70
Routing Resources 71
Health 73
Diagnostics 74
Discovery - Bonjour 74
Discovery - LLDP 74
Discovery - CDP 75
Ping 75
Traceroute 76
Chapter 7: Administration: Time Settings 78
System Time Options 78
SNTP Modes 80
Configuring System Time 80
Chapter 8: Administration: Diagnostics 89
Copper Ports Tests 89
Cisco 300 Series Managed Switches Administration Guide 2
Page 5

Contents
Displaying Optical Module Status 91
Configuring Port and VLAN Mirroring 92
Viewing CPU Utilization and Secure Core Technology 94
Chapter 9: Administration: Discovery 95
Bonjour 95
LLDP and CDP 97
Configuring LLDP 98
Configuring CDP 117
CDP Statistics 124
Chapter 10: Port Management 125
Configuring Ports 125
Loopback Detection 130
Link Aggregation 132
UDLD 139
PoE 139
Configuring Green Ethernet 139
Chapter 11: Port Management: Unidirectional Link Detection 146
UDLD Overview 146
UDLD Operation 147
Usage Guidelines 149
Dependencies On Other Features 149
Default Settings and Configuration 150
Before You Start 150
Common UDLD Tasks 150
Configuring UDLD 151
Chapter 12: Smartport 155
Cisco 300 Series Managed Switches Administration Guide 3
Page 6

Contents
Overview 156
What is a Smartport 156
Smartport Types 157
Smartport Macros 159
Macro Failure and the Reset Operation 160
How the Smartport Feature Works 161
Auto Smartport 161
Error Handling 165
Default Configuration 165
Relationships with Other Features and Backwards Compatibility 166
Common Smartport Tasks 166
Configuring Smartport Using The Web-based Interface 168
Built-in Smartport Macros 173
Chapter 13: Port Management: PoE 184
PoE on the Device 184
PoE Properties 187
PoE Settings 188
Chapter 14: VLAN Management 191
Overview 191
Regular VLANs 199
Private VLAN Settings 206
GVRP Settings 207
VLAN Groups 208
Voice VLAN 210
Access Port Multicast TV VLAN 222
Customer Port Multicast TV VLAN 225
Chapter 15: Spanning Tree 228
Cisco 300 Series Managed Switches Administration Guide 4
Page 7

Contents
STP Flavors 228
STP Status and Global Settings 229
Spanning Tree Interface Settings 231
Rapid Spanning Tree Settings 233
Multiple Spanning Tree 235
MSTP Properties 235
VLANs to a MSTP Instance 236
MSTP Instance Settings 237
MSTP Interface Settings 238
Chapter 16: Managing MAC Address Tables 241
Static MAC Addresses 242
Dynamic MAC Addresses 243
Reserved MAC Addresses 244
Chapter 17: Multicast 245
Multicast Forwarding 245
Multicast Properties 250
MAC Group Address 250
IP Multicast Group Addresses 252
IPv4 Multicast Configuration 253
IPv6 Multicast Configuration 256
IGMP/MLD Snooping IP Multicast Group 259
Multicast Router Ports 260
Forward All 260
Unregistered Multicast 261
Chapter 18: IP Configuration 263
Overview 263
IPv4 Management and Interfaces 266
Cisco 300 Series Managed Switches Administration Guide 5
Page 8

Contents
DHCP Server 283
IPv6 Management and Interfaces 291
Domain Name 304
Chapter 19: Security 309
Defining Users 310
Configuring TACACS+ 313
Configuring RADIUS 317
Management Access Method 321
Management Access Authentication 326
Secure Sensitive Data Management 327
SSL Server 327
SSH Server 329
SSH Client 330
Configuring TCP/UDP Services 330
Defining Storm Control 331
Configuring Port Security 332
802.1X 334
Denial of Service Prevention 334
DHCP Snooping 343
IP Source Guard 343
ARP Inspection 347
First Hop Security 352
Chapter 20: Security: 802.1X Authentication 353
Overview of 802.1X 353
Authenticator Overview 356
Common Tasks 364
802.1X Configuration Through the GUI 366
Defining Time Ranges 375
Cisco 300 Series Managed Switches Administration Guide 6
Page 9

Contents
Authentication Method and Port Mode Support 376
Chapter 21: Security: IPv6 First Hop Security 379
IPv6 First Hop Security Overview 380
Router Advertisement Guard 384
Neighbor Discovery Inspection 384
DHCPv6 Guard 385
Neighbor Binding Integrity 385
IPv6 Source Guard 388
Attack Protection 389
Policies, Global Parameters and System Defaults 390
Common Tasks 392
Default Settings and Configuration 394
Before You Start 394
Configuring IPv6 First Hop Security through Web GUI 395
Chapter 22: Security: Secure Sensitive Data Management 411
Introduction 411
SSD Rules 412
SSD Properties 417
Configuration Files 419
SSD Management Channels 423
Menu CLI and Password Recovery 424
Configuring SSD 424
Chapter 23: Security: SSH Client 428
Secure Copy (SCP) and SSH 428
Protection Methods 429
SSH Server Authentication 430
SSH Client Authentication 431
Cisco 300 Series Managed Switches Administration Guide 7
Page 10

Contents
Before You Begin 432
Common Tasks 432
SSH Client Configuration Through the GUI 434
Chapter 24: Security: SSH Server 438
Overview 438
Common Tasks 438
SSH Server Configuration Pages 439
Chapter 25: Access Control 443
Access Control Lists 443
MAC-based ACLs 446
IPv4-based ACLs 448
IPv6-Based ACLs 453
ACL Binding 456
Chapter 26: Quality of Service 459
QoS Features and Components 460
Configuring QoS - General 462
QoS Basic Mode 471
QoS Advanced Mode 473
Managing QoS Statistics 483
Chapter 27: SNMP 487
SNMP Versions and Workflow 487
Model OIDs 490
SNMP Engine ID 491
Configuring SNMP Views 493
Creating SNMP Groups 494
Managing SNMP Users 496
Cisco 300 Series Managed Switches Administration Guide 8
Page 11

Contents
Defining SNMP Communities 497
Defining Trap Settings 499
Notification Recipients 499
SNMP Notification Filters 503
Cisco 300 Series Managed Switches Administration Guide 9
Page 12

Getting Started
This section provides an introduction to the web-based configuration utility, and
covers the following topics:
• Starting the Web-based Configuration Utility
• Quick Start Device Configuration
• Interface Naming Conventions
1
• Window Navigation
Starting the Web-based Configuration Utility
This section describes how to navigate the web-based switch configuration utility.
If you are using a pop-up blocker, make sure it is disabled.
Browser Restrictions
If you are using IPv6 interfaces on your management station, use the IPv6 global
address and not the IPv6 link local address to access the device from your
browser.
Launching the Configuration Utility
To open the web-based configuration utility:
STEP 1 Open a Web browser.
STEP 2 Enter the IP address of the device you are configuring in the address bar on the
browser, and then press Enter.
Cisco 300 Series Managed Switches Administration Guide 10
Page 13

1
Getting Started
Starting the Web-based Configuration Utility
NOTE When the device is using the factory default IP address of 192.168.1.254, its power
LED flashes continuously. When the device is using a DHCP-assigned IP address or
an administrator-configured static IP address, the power LED is on solid.
Logging In
The default username is cisco and the default password is cisco. The first time
that you log in with the default username and password, you are required to enter
a new password.
NOTE If you have not previously selected a language for the GUI, the language of the Login
page is determined by the language(s) requested by your browser and the
languages configured on your device. If your browser requests Chinese, for
example, and Chinese has been loaded into your device, the Login page is
automatically displayed in Chinese. If Chinese has not been loaded into your
device, the Login page appears in English.
The languages loaded into the device have a language and country code (en-US,
en-GB and so on). For the Login page to be automatically displayed in a particular
language, based on the browser request, both the language and country code of
the browser request must match those of the language loaded on the device. If the
browser request contains only the language code without a country code (for
example: fr). The first embedded language with a matching language code is
taken (without matching the country code, for example: fr_CA).
To log in to the device configuration utility:
STEP 1 Enter the username/password. The password can contain up to 64 ASCII
characters. Password-complexity rules are described in Setting Password
Complexity Rules.
STEP 2 If you are not using English, select the desired language from the Language drop-
down menu. To add a new language to the device or update a current one, see
Upgrade/Backup Firmware/Language.
STEP 3 If this is the first time that you logged on with the default user ID (cisco) and the
default password (cisco) or your password has expired, the Change Password
Page appears. See Password Expiration for additional information.
STEP 4 Choose whether to select Disable Password Complexity Enforcement or not.
For more information on password complexity, see the Setting Password
Complexity Rules section.
STEP 5 Enter the new password and click Apply.
11 Cisco 300 Series Managed Switches Administration Guide
Page 14

Getting Started
!
Starting the Web-based Configuration Utility
When the login attempt is successful, the Getting Started page appears.
If you entered an incorrect username or password, an error message appears and
the Login page remains displayed on the window. If you are having problems
logging in, please see the Launching the Configuration Utility section in the
Administration Guide for additional information.
Select Don't show this page on startup to prevent the Getting Started page from
being displayed each time that you log on to the system. If you select this option,
the System Summary page is opened instead of the Getting Started page.
HTTP/HTTPS
You can either open an HTTP session (not secured) by clicking Log In, or you can
open an HTTPS (secured) session, by clicking Secure Browsing (HTTPS). You are
asked to approve the logon with a default RSA key, and an HTTPS session is
opened.
1
NOTE There is no need to input the username/password prior to clicking the Secure
Browsing (HTTPS) button.
For information on how to configure HTTPS, see SSL Server.
Password Expiration
The New Password page is displayed in the following cases:
• The first time that you access the device with the default username cisco
and password cisco. This page forces you to replace the factory default
password.
• When the password expires, this page forces you to select a new
password.
Logging Out
By default, the application logs out after ten minutes of inactivity. You can change
this default value as described in the Defining Idle Session Timeout section.
CAUTION Unless the Running Configuration is copied to the Startup Configuration, rebooting
the device removes all changes made since the last time the file was saved. Save
the Running Configuration to the Startup Configuration before logging off to
preserve any changes you made during this session.
A flashing red X icon to the left of the Save application link indicates that Running
Cisco 300 Series Managed Switches Administration Guide 12
Page 15

1
Getting Started
Starting the Web-based Configuration Utility
Configuration changes have not yet been saved to the Startup Configuration file.
The flashing can be disabled by clicking on the Disable Save Icon Blinking button
on the Copy/Save Configuration page
When the device auto-discovers a device, such as an IP phone (see What is a
Smartport), and it configures the port appropriately for the device. These
configuration commands are written to the Running Configuration file. This causes
the Save icon to begin blinking when the you log on, even though you did not make
any configuration changes.
When you click Save, the Copy/Save Configuration page appears. Save the
Running Configuration file by copying it to the Startup Configuration file. After this
save, the red X icon and the Save application link are no longer displayed.
To l o g o u t , c li ck Logout in the top right corner of any page. The system logs out of
the device.
When a timeout occurs or you intentionally log out of the system, a message is
displayed and the Login page appears, with a message indicating the logged-out
state. After you log in, the application returns to the initial page.
The initial page displayed depends on the “Do not show this page on startup”
option in the Getting Started page. If you did not select this option, the initial page
is the Getting Started page. If you did select this option, the initial page is the
System Summary page.
13 Cisco 300 Series Managed Switches Administration Guide
Page 16

Getting Started
Quick Start Device Configuration
Quick Start Device Configuration
To simplify device configuration through quick navigation, the Getting Started
page provides links to the most commonly used pages.
Category Link Name (on the Page) Linked Page
1
Change Management
Applications and Services
Change Device IP Address IPv4 Interface page
Create VLAN Create VLAN page
Configure Port Settings Port Setting page
Device Status System Summary System Summary page
Port Statistics Interface page
RMON Statistics Statistics page
View Log RAM Memory page
Quick Access Change Device Password User Accounts page
Upgrade Device Software Upgrade/Backup Firmware/
Backup Device Configuration Download/Backup
Create MAC Based ACL MAC Based ACL page
TCP/UDP Services page
Language page
Configuration/Log page
Create IP Based ACL IPv4 Based ACL page
Configure QoS QoS Properties page
Configure Port Mirroring Port and VLAN Mirroring page
There are two hot links on the Getting Started page that take you to Cisco web
pages for more information. Clicking on the Support link takes you to the device
product support page, and clicking on the Forums link takes you to the Support
Community page.
Cisco 300 Series Managed Switches Administration Guide 14
Page 17

1
Interface Naming Conventions
Within the GUI, interfaces are denoted by concatenating the following elements:
• Type of interface: The following types of interfaces are found on the various
types of devices:
- Fast Ethernet (10/100 bits)—These are displayed as FE.
- Gigabit Ethernet ports (10/100/1000 bits)—These are displayed as
GE.
- LAG (Port Channel)—These are displayed as LAG.
- VLAN—These are displayed as VLAN.
- Tunnel —These are displayed as Tunnel.
Getting Started
Interface Naming Conventions
• Interface Number: Port, LAG, tunnel or VLAN ID
15 Cisco 300 Series Managed Switches Administration Guide
Page 18

Getting Started
Window Navigation
Window Navigation
This section describes the features of the web-based switch configuration utility.
Application Header
The Application Header appears on every page. It provides the following
application links:
1
Application Link
Name
Username Displays the name of the user logged on to the device. The
Description
A flashing red X icon displayed to the left of the Save
application link indicates that Running Configuration
changes have been made that have not yet been saved to
the Startup Configuration file. The flashing of the red X can
be disabled on the Copy/Save Configuration page.
Click Save to display the Copy/Save Configuration page.
Save the Running Configuration file by copying it to the
Startup Configuration file type on the device. After this
save, the red X icon and the Save application link are no
longer displayed. When the device is rebooted, it copies
the Startup Configuration file type to the Running
Configuration and sets the device parameters according
to the data in the Running Configuration.
default username is cisco. (The default password is cisco).
Cisco 300 Series Managed Switches Administration Guide 16
Page 19

1
Getting Started
Window Navigation
Application Link
Name
Language Menu This menu provides the following options:
Description
• Select a language: Select one of the languages that
appear in the menu. This language will be the webbased configuration utility language.
• Download Language: Add a new language to the
device.
• Delete Language: Deletes the second language on
the device. The first language (English) cannot be
deleted.
• Debug: Used for translation purposes. If you select
this option, all web-based configuration utility labels
disappear and in their place are the IDs of the
strings that correspond to the IDs in the language
file.
NOTE To upgrade a language file, use the Upgrade/
Backup Firmware/Language page.
Logout Click to log out of the web-based switch configuration
utility.
About Click to display the device name and device version
number.
Help Click to display the online help.
The SYSLOG Alert Status icon appears when a SYSLOG
message, above the critical severity level, is logged. Click
the icon to open the RAM Memory page. After you access
this page, the SYSLOG Alert Status icon is no longer
displayed. To display the page when there is not an active
SYSLOG message, Click Status and Statistics > View
Log > RAM Memory.
17 Cisco 300 Series Managed Switches Administration Guide
Page 20

Getting Started
Window Navigation
1
Management Buttons
The following table describes the commonly-used buttons that appear on various
pages in the system.
Button Name Description
Use the pull-down menu to configure the number of
entries per page.
Indicates a mandatory field.
Add Click to display the related Add page and add an entry to a
table. Enter the information and click Apply to save it to the
Running Configuration. Click Close to return to the main
page. Click Save to display the Copy/Save Configuration
page and save the Running Configuration to the Startup
Configuration file type on the device.
Apply Click to apply changes to the Running Configuration on the
device. If the device is rebooted, the Running
Configuration is lost, unless it is saved to the Startup
Configuration file type or another file type. Click Save to
display the Copy/Save Configuration page and save the
Running Configuration to the Startup Configuration file
type on the device.
Cancel Click to reset changes made on the page.
Clear All
Interfaces
Counters
Clear Interface
Counters
Clear Logs Clears log files.
Clear Table Clears table entries.
Close Returns to main page. If any changes were not applied to
Click to clear the statistic counters for all interfaces.
Click to clear the statistic counters for the selected
interface.
the Running Configuration, a message appears.
Cisco 300 Series Managed Switches Administration Guide 18
Page 21

1
Getting Started
Window Navigation
Button Name Description
Copy Settings A table typically contains one or more entries containing
configuration settings. Instead of modifying each entry
individually, it is possible to modify one entry and then
copy the selected entry to multiple entries, as described
below:
1. Select the entry to be copied. Click Copy Settings to
display the popup.
2. Enter the destination entry numbers in the to field.
3. Click Apply to save the changes and click Close to
return to the main page.
Delete After selecting an entry in the table, click Delete to
remove.
Details Click to display the details associated with the entry
selected.
Edit Select the entry and click Edit. The Edit page appears,
and the entry can be modified.
1. C li ck Apply to save the changes to the Running
Configuration.
2. Click Close to return to the main page.
Go Enter the query filtering criteria and click Go. The results
are displayed on the page.
Refresh Clich Refresh to refresh the counter values.
Te st Click Te st to perform the related tests.
19 Cisco 300 Series Managed Switches Administration Guide
Page 22

Getting Started
Window Navigation
1
Cisco 300 Series Managed Switches Administration Guide 20
Page 23

1
Getting Started
Window Navigation
21 Cisco 300 Series Managed Switches Administration Guide
Page 24

Status and Statistics
This section describes how to view device statistics.
It covers the following topics:
• System Summary
• Ethernet Interfaces
• Etherlike Statistics
2
• GVRP Statistics
• 802.1X EAP Statistics
• ACL Statistics
• TCAM Utilization
• Health
• RMON
• View Log
System Summary
See System Settings.
Ethernet Interfaces
The Interface page displays traffic statistics per port. The refresh rate of the
information can be selected.
This page is useful for analyzing the amount of traffic that is both sent and
received and its dispersion (Unicast, Multicast, and Broadcast).
Cisco 300 Series Managed Switches Administration Guide 22
Page 25

2
Status and Statistics
Ethernet Interfaces
To display Ethernet statistics and/or set the refresh rate:
STEP 1 Click Status and Statistics > Interface.
STEP 2 Enter the parameters.
• Interface—Select the type of interface and specific interface for which
Ethernet statistics are to be displayed.
• Refresh Rate—Select the time period that passes before the interface
Ethernet statistics are refreshed.
The Receive Statistics area displays information about incoming packets.
• Tot al B y te s (O ct et s)—Octets received, including bad packets and FCS
octets, but excluding framing bits.
• Unicast Packets—Good Unicast packets received.
• Multicast Packets—Good Multicast packets received.
• Broadcast Packets—Good Broadcast packets received.
• Packets with Errors—Packets with errors received.
The Transmit Statistics area displays information about outgoing packets.
• Tot al B y te s (O ct et s)—Octets transmitted, including bad packets and FCS
octets, but excluding framing bits.
• Unicast Packets—Good Unicast packets transmitted.
• Multicast Packets—Good Multicast packets transmitted.
• Broadcast Packets—Good Broadcast packets transmitted.
To clear or view statistics counters:
• Click Clear Interface Counters to clear counters for the interface displayed.
• Click View All Interfaces Statistics to see all ports on a single page.
23 Cisco 300 Series Managed Switches Administration Guide
Page 26

Status and Statistics
Etherlike Statistics
Etherlike Statistics
The Etherlike page displays statistics per port according to the Etherlike MIB
standard definition. The refresh rate of the information can be selected. This page
provides more detailed information regarding errors in the physical layer (Layer 1)
that might disrupt traffic.
To view Etherlike Statistics and/or set the refresh rate:
STEP 1 Click Status and Statistics > Etherlike.
STEP 2 Enter the parameters.
• Interface—Select the type of interface and specific interface for which
2
Ethernet statistics are to be displayed.
• Refresh Rate—Select the amount of time that passes before the Etherlike
statistics are refreshed.
The fields are displayed for the selected interface.
• Frame Check Sequence (FCS) Errors—Received frames that failed the
CRC (cyclic redundancy checks).
• Single Collision Frames—Frames that were involved in a single collision,
but were successfully transmitted.
• Late Collisions—Collisions that have been detected after the first 512 bits
of data.
• Excessive Collisions—Transmissions rejected due to excessive collisions.
• Oversize Packets—Packets greater than 2000 octets received.
• Internal MAC Receive Errors—Frames rejected because of receiver errors.
• Pause Frames Received—Received flow control pause frames.
• Pause Frames Transmitted—Flow control pause frames transmitted from
the selected interface.
To clear statistics counters:
• Click Clear Interface Counters to clear the selected interfaces counters.
• Click View All Interfaces Statistics to see all ports on a single page.
Cisco 300 Series Managed Switches Administration Guide 24
Page 27

2
GVRP Statistics
The GVRP page displays information regarding GARP VLAN Registration Protocol
(GVRP) frames that were sent or received from a port. GVRP is a standards-based
Layer 2 network protocol, for automatic configuration of VLAN information on
switches. It is defined in the 802.1ak amendment to 802.1Q-2005.
GVRP statistics for a port are only displayed if GVRP is enabled globally and on
the port. See the GVRP page.
To view GVRP statistics and/or set the refresh rate:
STEP 1 Click Status and Statistics > GVRP.
STEP 2 Enter the parameters.
Status and Statistics
GVRP Statistics
• Interface—Select the specific interface for which GVRP statistics are to be
displayed.
• Refresh Rate—Select the time period that passes before the GVRP
statistics page is refreshed.
The Attribute Counter block displays the counters for various types of packets per
interface.
• Join Empty—GVRP Join Empty packets received/transmitted.
• Empty—GVRP empty packets received/transmitted.
• Leave Empty—GVRP Leave Empty packets received/transmitted.
• Join In—GVRP Join In packets received/transmitted.
• Leave In—GVRP Leave In packets received/transmitted.
• Leave All—GVRP Leave All packets received/transmitted.
The GVRP Error Statistics section displays the GVRP error counters.
• Invalid Protocol ID—Invalid protocol ID errors.
• Invalid Attribute Type—Invalid attribute ID errors.
• Invalid Attribute Value—Invalid attribute value errors.
• Invalid Attribute Length—Invalid attribute length errors.
• Invalid Event—Invalid events.
25 Cisco 300 Series Managed Switches Administration Guide
Page 28

Status and Statistics
802.1X EAP Statistics
To clear statistics counters:
• Click Clear Interface Counters to clear the selected counters.
• Click View All Interfaces Statistics to see all ports on a single page.
802.1X EAP Statistics
The 802.1x EAP page displays detailed information regarding the EAP (Extensible
Authentication Protocol) frames that were sent or received. To configure the
802.1X feature, see the 802.1X Properties page.
To view the EAP Statistics and/or set the refresh rate:
2
STEP 1 Click Status and Statistics > 802.1x EAP.
STEP 2 Select the Interface that is polled for statistics.
STEP 3 Select the Refresh Rate (time period) that passes before the EAP statistics are
refreshed.
The values are displayed for the selected interface.
• EAPOL Frames Received—Valid EAPOL frames received on the port.
• EAPOL Frames Transmitted—Valid EAPOL frames transmitted by the port.
• EAPOL Start Frames Received—EAPOL Start frames received on the port.
• EAPOL Logoff Frames Received—EAPOL Logoff frames received on the
port.
• EAP Response/ID Frames Received—EAP Resp/ID frames received on the
port.
• EAP Response Frames Received—EAP Response frames received by the
port (other than Resp/ID frames).
• EAP Request/ID Frames Transmitted—EAP Req/ID frames transmitted by
the port.
• EAP Request Frames Transmitted—EAP Request frames transmitted by
the port.
Cisco 300 Series Managed Switches Administration Guide 26
Page 29

2
Status and Statistics
ACL Statistics
• Invalid EAPOL Frames Received—Unrecognized EAPOL frames received
on this port.
• EAP Length Error Frames Received—EAPOL frames with an invalid Packet
Body Length received on this port.
• Last EAPOL Frame Version—Protocol version number attached to the most
recently received EAPOL frame.
• Last EAPOL Frame Source—Source MAC address attached to the most
recently received EAPOL frame.
To clear statistics counters:
• Click Clear Interface Counters to clear the selected interfaces counters.
• Click Refresh to refresh the selected interfaces counters.
• Click View All Interfaces Statistics to clear the counters of all interfaces.
ACL Statistics
STEP 1 Click Status and Statistics > ACL.
STEP 2 Select the Refresh Rate (time period in seconds) that passes before the page is
When the ACL logging feature is enabled, an informational SYSLOG message is
generated for packets that match ACL rules.
To view the interfaces on which packets were forward or rejected based on ACLs:
refreshed. A new group of interfaces is created for each time period.
The interfaces on which packets were forwarded or rejected based on ACL rules
are displayed.
To manage statistics counters:
• Click Refresh to reset the counters.
• Click Clear Counters to clear the counters of all interfaces.
27 Cisco 300 Series Managed Switches Administration Guide
Page 30

Status and Statistics
TCAM Utilization
TCAM Utilization
The device architecture uses a Ternary Content Addressable Memory (TCAM) to
support packet actions in wire speed.
TCAM holds the rules produced by applications, such as ACLs (Access Control
Lists), Quality of Service (QoS), IP Routing and user-created rules.
Some applications allocate rules upon their initiation. Additionally, processes that
initialize during system boot use some of their rules during the startup process.
To view TCAM utilization, click Status and Statistics > TCAM Utilization.
The TCAM Utilization page shows the following fields:
2
• Maximum TCAM Entries for IPv4 and Non-IP—Maximum TCAM entries
available.
Health
• IPv4 Routing
- In Use—Number of TCAM entries used for IPv4 routing.
- Maximum—Number of available TCAM entries that can be used for IPv4
routing.
• Non-IP Rules
- In Use—Number of TCAM entries used for non-IP rules.
- Maximum—Number of available TCAM entries that can be used for non-
IP rules.
See Health.
Cisco 300 Series Managed Switches Administration Guide 28
Page 31
2
RMON
Status and Statistics
RMON
RMON (Remote Networking Monitoring) enables an SNMP agent in the device to
proactively monitor traffic statistics over a given period and send traps to an
SNMP manager. The local SNMP agent compares actual, real-time counters
against predefined thresholds and generates alarms, without the need for polling
by a central SNMP management platform. This is an effective mechanism for
proactive management, provided that you have set the correct thresholds relative
to your network’s base line.
RMON decreases the traffic between the manager and the device since the
SNMP manager does not have to poll the device frequently for information, and
enables the manager to get timely status reports, since the device reports events
as they occur.
With this feature, you can perform the following actions:
• View the current statistics (from the time that the counter values were
cleared). You can also collect the values of these counters over a period of
time, and then view the table of collected data, where each collected set is
a single line of the History tab.
• Define interesting changes in counter values, such as “reached a certain
number of late collisions” (defines the alarm), and then specify what action
to perform when this event occurs (log, trap, or log and trap).
RMON Statistics
The Statistics page displays detailed information regarding packet sizes and
information regarding physical layer errors. The information is displayed according
to the RMON standard. An oversized packet is defined as an Ethernet frame with
the following criteria:
• Packet length is greater than MRU byte size.
• Collision event has not been detected.
• Late collision event has not been detected.
• Received (Rx) error event has not been detected.
• Packet has a valid CRC.
29 Cisco 300 Series Managed Switches Administration Guide
Page 32
Status and Statistics
RMON
STEP 1 Click Status and Statistics > RMON > Statistics.
STEP 2 Select the Interface for which Ethernet statistics are to be displayed.
STEP 3 Select the Refresh Rate, which is the time period that passes before the interface
2
To view RMON statistics and/or set the refresh rate:
statistics are refreshed.
The following statistics are displayed for the selected interface.
• Bytes Received—Octets received, including bad packets and FCS octets,
but excluding framing bits.
• Drop Events—Packets dropped.
• Packets Received—Good packets received, including Multicast and
Broadcast packets.
• Broadcast Packets Received—Good Broadcast packets received. This
number does not include Multicast packets.
• Multicast Packets Received—Good Multicast packets received.
• CRC & Align Errors—CRC and Align errors that have occurred.
• Undersize Packets—Undersized packets (less than 64 octets) received.
• Oversize Packets—Oversized packets (over 2000 octets) received.
• Fragments—Fragments (packets with less than 64 octets, excluding
framing bits, but including FCS octets) received.
• Jabbers—Received packets that were longer than 1632 octets. This
number excludes frame bits, but includes FCS octets that had either a bad
FCS (Frame Check Sequence) with an integral number of octets (FCS Error)
or a bad FCS with a non-integral octet (Alignment Error) number. A Jabber
packet is defined as an Ethernet frame that satisfies the following criteria:
- Packet data length is greater than MRU.
- Packet has an invalid CRC.
- Received (Rx) Error Event has not been detected.
• Collisions—Collisions received. If Jumbo frames are enabled, the threshold
of Jabber frames is raised to the maximum size of Jumbo frames.
• Frames of 64 Bytes—Frames, containing 64 bytes that were received.
Cisco 300 Series Managed Switches Administration Guide 30
Page 33
2
Status and Statistics
RMON
• Frames of 65 to 127 Bytes—Frames, containing 65-127 bytes that were
received.
• Frames of 128 to 255 Bytes—Frames, containing 128-255 bytes that were
received.
• Frames of 256 to 511 Bytes—Frames, containing 256-511 bytes that were
received.
• Frames of 512 to 1023 Bytes—Frames, containing 512-1023 bytes that
were received.
• Frames of 1024 Bytes or More—Frames, containing 1024-2000 bytes, and
Jumbo Frames, that were received.
To clear statistics counters:
• Click Clear Interface Counters to clear the selected interfaces counters.
• Click View All Interfaces Statistics to see all ports on a single page.
RMON History
The RMON feature enables monitoring statistics per interface.
The History Control Table page
samples to store and the port from which to gather the data.
After the data is sampled and stored, it appears in the History Table page that can
be viewed by clicking History Table.
To enter RMON control information:
STEP 1 Click Status and Statistics > RMON > History. The fields displayed on this page
are defined in the Add RMON History page, below. The only field is that is on this
page and not defined in the Add page is:
• Current Number of Samples—RMON is allowed by the standard to not
grant all requested samples, but rather to limit the number of samples per
request. Therefore, this field represents the sample number actually granted
to the request that is equal or less than the requested value.
defines the sampling frequency, amount of
STEP 2 Click Add.
STEP 3 Enter the parameters.
• New History Entry—Displays the number of the new History table entry.
31 Cisco 300 Series Managed Switches Administration Guide
Page 34
Status and Statistics
RMON
2
• Source Interface—Select the type of interface from which the history
samples are to be taken.
• Max No. of Samples to Keep—Enter the number of samples to store.
• Sampling Interval—Enter the time in seconds that samples are collected
from the ports. The field range is 1-3600.
• Owner—Enter the RMON station or user that requested the RMON
information.
STEP 4 Click Apply. The entry is added to the History Control Table page
Configuration file is updated.
STEP 5 Click History Table (described below) to view the actual statistics.
,
and the Running
RMON History Table
The History Table page displays interface-specific statistical network samplings.
The samples were configured in the History Control table described above.
To view RMON history statistics:
STEP 1 Click Status and Statistics > RMON > History.
STEP 2 Click History Table.
STEP 3 From the History Entry No. drop down menu, optionally select the entry number
of the sample to display.
The fields are displayed for the selected sample.
• Owner—History table entry owner.
• Sample No.—Statistics were taken from this sample.
• Drop Events—Dropped packets due to lack of network resources during the
sampling interval. This may not represent the exact number of dropped
packets, but rather the number of times dropped packets were detected.
• Bytes Received—Octets received including bad packets and FCS octets,
but excluding framing bits.
• Packets Received—Packets received, including bad packets, Multicast,
and Broadcast packets.
Cisco 300 Series Managed Switches Administration Guide 32
Page 35
2
Status and Statistics
RMON
• Broadcast Packets—Good Broadcast packets excluding Multicast packets.
• Multicast Packets—Good Multicast packets received.
• CRC Align Errors—CRC and Align errors that have occurred.
• Undersize Packets—Undersized packets (less than 64 octets) received.
• Oversize Packets—Oversized packets (over 2000 octets) received.
• Fragments—Fragments (packets with less than 64 octets) received,
excluding framing bits, but including FCS octets.
• Jabbers—Total number of received packets that were longer than 2000
octets. This number excludes frame bits, but includes FCS octets that had
either a bad FCS (Frame Check Sequence) with an integral number of octets
(FCS Error) or a bad FCS with a non-integral octet (Alignment Error) number.
• Collisions—Collisions received.
• Utilization—Percentage of current interface traffic compared to maximum
traffic that the interface can handle.
RMON Events Control
You can control the occurrences that trigger an alarm and the type of notification
that occurs. This is performed as follows:
• Events Page—Configures what happens when an alarm is triggered. This
can be any combination of logs and traps.
• Alarms Page—Configures the occurrences that trigger an alarm.
To define RMON events:
STEP 1 Click Status and Statistics > RMON > Events.
This page displays previously defined events.
The fields on this page are defined by the Add RIMON Events dialog box except
for the Time field.
• Time—Displays the time of the event. (This is a read-only table in the parent
window and cannot be defined).
STEP 2 Click Add.
33 Cisco 300 Series Managed Switches Administration Guide
Page 36
Status and Statistics
RMON
STEP 3 Enter the parameters.
2
• Event Entry—Displays the event entry index number for the new entry.
• Community—Enter the SNMP community string to be included when traps
are sent (optional). Note that the community must be defined using the
Defining SNMPv1,2 Notification Recipients or Defining SNMPv3
Notification Recipients pages for the trap to reach the Network
Management Station.
• Description—Enter a name for the event. This name is used in the Add
RMON Alarm page to attach an alarm to an event.
• Notification Type—Select the type of action that results from this event.
Values are:
- None—No action occurs when the alarm goes off.
- Log (Event Log Table)—Add a log entry to the Event Log table when the
alarm is triggered.
- Trap (SNMP Manager and SYSLOG Server)—Send a trap to the remote
log server when the alarm goes off.
- Log and Trap—Add a log entry to the Event Log table and send a trap to
the remote log server when the alarm goes off.
• Owner—Enter the device or user that defined the event.
STEP 4 Click Apply. The RMON event is saved to the Running Configuration file.
STEP 5 Click Event Log Table to display the log of alarms that have occurred and that have
been logged (see description below).
RMON Events Logs
The Event Log Table page displays the log of events (actions) that occurred. Two
types of events can be logged: Log or Log and Trap. The action in the event is
performed when the event is bound to an alarm (see the Alarms page) and the
conditions of the alarm have occurred.
STEP 1 Click Status and Statistics > RMON > Events.
STEP 2 Click Event Log Table.
Cisco 300 Series Managed Switches Administration Guide 34
Page 37
2
Status and Statistics
RMON
This page displays the following fields:
• Event Entry No.—Event’s log entry number.
• Log No.—Log number (within the event).
• Log Time—Time that the log entry was entered.
• Description—Description of event that triggered the alarm.
RMON Alarms
RMON alarms provide a mechanism for setting thresholds and sampling intervals
to generate exception events on counters or any other SNMP object counter
maintained by the agent. Both the rising and falling thresholds must be configured
in the alarm. After a rising threshold is crossed, no rising events are generated until
the companion falling threshold is crossed. After a falling alarm is issued, the next
alarm is issued when a rising threshold is crossed.
One or more alarms are bound to an event, which indicates the action to be taken
when the alarm occurs.
Alarm counters can be monitored by either absolute values or changes (delta) in
the counter values.
To enter RMON alarms:
STEP 1 Click Status and Statistics > RMON > Alarms. All previously-defined alarms are
displayed. The fields are described in the Add RMON Alarm page below. In
addition to those fields, the following field appears:
• Counter Value—Displays the value of the statistic during the last sampling
period.
STEP 2 Click Add.
STEP 3 Enter the parameters.
• Alarm Entry No.—Displays the alarm entry number.
• Interface—Select the type of interface for which RMON statistics are
displayed.
• Counter Name—Select the MIB variable that indicates the type of
occurrence measured.
35 Cisco 300 Series Managed Switches Administration Guide
Page 38
Status and Statistics
View Log
2
• Counter Value—Number of occurrences.
• Sample Type—Select the sampling method to generate an alarm. The
options are:
- Absolute—If the threshold is crossed, an alarm is generated.
- Delta—Subtracts the last sampled value from the current value. The
difference in the values is compared to the threshold. If the threshold was
crossed, an alarm is generated.
• Rising Threshold—Enter the value that triggers the rising threshold alarm.
• Rising Event—Select an event to be performed when a rising event is
triggered. Events are created in the Events page.
• Falling Threshold—Enter the value that triggers the falling threshold alarm.
• Falling Event—Select an event to be performed when a falling event is
triggered.
View Log
• Startup Alarm—Select the first event from which to start generation of
alarms. Rising is defined by crossing the threshold from a low-value
threshold to a higher-value threshold.
- Rising Alarm—A rising value triggers the rising threshold alarm.
- Falling Alarm—A falling value triggers the falling threshold alarm.
- Rising and Falling—Both rising and falling values trigger the alarm.
• Interval—Enter the alarm interval time in seconds.
• Owner—Enter the name of the user or network management system that
receives the alarm.
STEP 4 Click Apply. The RMON alarm is saved to the Running Configuration file.
See Viewing Memory Logs.
Cisco 300 Series Managed Switches Administration Guide 36
Page 39
2
Status and Statistics
View Log
37 Cisco 300 Series Managed Switches Administration Guide
Page 40
Administration: System Log
This section describes the system logging, which enables the device to generate
multiple independent logs. Each log is a set of messages describing system
events.
The device generates the following local logs:
• Log sent to the console interface.
3
• Log written into a cyclical list of logged events in the RAM and erased when
the device reboots.
• Log written to a cyclical log-file saved to the Flash memory and persists
across reboots.
In addition, you can send messages to remote SYSLOG servers in the form of
SNMP traps and SYSLOG messages.
This section covers the following sections:
• Setting System Log Settings
• Setting Remote Logging Settings
• Viewing Memory Logs
Setting System Log Settings
You can select the events to be logged by severity level. Each log message has a
severity level marked with the first letter of the severity level concatenated with a
dash (-) on each side (except for Emergency that is indicated by the letter F). For
example, the log message "%INIT-I-InitCompleted: … " has a severity level of I,
meaning Informational.
Cisco 300 Series Managed Switches Administration Guide 38
Page 41
3
Administration: System Log
Setting System Log Settings
The event severity levels are listed from the highest severity to the lowest severity,
as follows:
• Emergency—System is not usable.
• Alert—Action is needed.
• Critical—System is in a critical condition.
• Error—System is in error condition.
• Warning—System warning has occurred.
• Notice—System is functioning properly, but a system notice has occurred.
• Informational—Device information.
• Debug—Detailed information about an event.
You can select different severity levels for RAM and Flash logs. These logs are
displayed in the RAM Memory page and Flash Memory page, respectively.
Selecting a severity level to be stored in a log causes all of the higher severity
events to be automatically stored in the log. Lower severity events are not stored
in the log.
For example, if Warning is selected, all severity levels that are Warning and higher
are stored in the log (Emergency, Alert, Critical, Error, and Warning). No events with
severity level below Warning are stored (Notice, Informational, and Debug).
To set global log parameters:
STEP 1 Click Administration > System Log > Log Settings.
STEP 2 Enter the parameters.
• Logging—Select to enable message logging.
• Syslog Aggregator—Select to enable the aggregation of SYSLOG
messages and traps. If enabled, identical and contiguous SYSLOG
messages and traps are aggregated over the specified Max. Aggregation
Time and sent in a single message. The aggregated messages are sent in
the order of their arrival. Each message states the number of times it was
aggregated.
• Max. Aggregation Time—Enter the interval of time that SYSLOG messages
are aggregated.
39 Cisco 300 Series Managed Switches Administration Guide
Page 42
Administration: System Log
Setting Remote Logging Settings
3
• Originator Identifier—Enables adding an origin identifier to SYSLOG
messages. The options are:
- None—Do not include the origin identifier in SYSLOG messages.
- Hostname—Include the system host name in SYSLOG messages.
- IPv4 Address—Include the IPv4 address of the sending interface in
SYSLOG messages.
- IPv6 Address—Include the IPv6 address of the sending interface in
SYSLOG messages.
- User Defined—Enter a description to be included in SYSLOG messages.
• RAM Memory Logging—Select the severity levels of the messages to be
logged to the RAM.
• Flash Memory Logging—Select the severity levels of the messages to be
logged to the Flash memory.
STEP 3 Click Apply. The Running Configuration file is updated.
Setting Remote Logging Settings
The Remote Log Servers page enables defining remote SYSLOG servers to which
log messages are sent. For each server, you can configure the severity of the
messages that it receives.
To d e f i n e S YS LO G s er v e r s :
STEP 1 Click Administration > System Log > Remote Log Servers.
STEP 2 Enter the following fields:
• IPv4 Source Interface—Select the source interface whose IPv4 address
will be used as the source IPv4 address of SYSLOG messages sent to
SYSLOG servers.
• IPv6 Source Interface—Select the source interface whose IPv6 address
will be used as the source IPv6 address of SYSLOG messages sent to
SYSLOG servers.
Cisco 300 Series Managed Switches Administration Guide 40
Page 43
3
Administration: System Log
Setting Remote Logging Settings
NOTE If the Auto option is selected, the system takes the source IP address
from the IP address defined on the outgoing interface.
Information is described for each previously-configured log server. The fields are
described below in the Add page.
STEP 3 Click Add.
STEP 4 Enter the parameters.
• Server Definition—Select whether to identify the remote log server by IP
address or name.
• IP Version—Select the supported IP format.
• IPv6 Address Type—Select the IPv6 address type (if IPv6 is used). The
options are:
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
• Link Local Interface—Select the link local interface (if IPv6 Address Type
Link Local is selected) from the list.
• Log Server IP Address/Name—Enter the IP address or domain name of the
log server.
• UDP Port—Enter the UDP port to which the log messages are sent.
• Facility—Select a facility value from which system logs are sent to the
remote server. Only one facility value can be assigned to a server. If a second
facility code is assigned, the first facility value is overridden.
• Description—Enter a server description.
• Minimum Severity—Select the minimum level of system log messages to
be sent to the server.
STEP 5 Click Apply. The Add Remote Log Server page
added, and the Running Configuration file is updated.
closes, the SYSLOG server is
41 Cisco 300 Series Managed Switches Administration Guide
Page 44
Administration: System Log
Viewing Memor y Logs
Viewing Memory Logs
The device can write to the following logs:
• Log in RAM (cleared during reboot).
• Log in Flash memory (cleared only upon user command).
You can configure the messages that are written to each log by severity, and a
message can go to more than one log, including logs that reside on external
SYSLOG servers.
RAM Memory
The RAM Memory page displays all messages that were saved in the RAM
(cache) in chronological order. Entries are stored in the RAM log according to the
configuration in the Log Settings page.
3
To view log entries, click Status and Statistics > View Log > RAM Memory.
The top of the page has a button that allows you to Disable Alert Icon Blinking.
Click. This button toggles between disable and enable.
The Current Logging Threshold specifies the levels of logging that are
generated. This can be changed by clicking Edit by the field’s name.
This page contains the following fields for every log file:
• Log Index—Log entry number.
• Log Time—Time when message was generated.
• Severity—Event severity.
• Description—Message text describing the event.
To clear the log messages, click Clear Logs. The messages are cleared.
Flash Memory
The Flash Memory page displays the messages that were stored in the Flash
memory, in chronological order. The minimum severity for logging is configured in
the Log Settings page. Flash logs remain when the device is rebooted. You can
clear the logs manually.
To view the Flash logs, click Status and Statistics > View Log > Flash Memory.
Cisco 300 Series Managed Switches Administration Guide 42
Page 45
3
Administration: System Log
Viewing Memory Logs
The Current Logging Threshold specifies the levels of logging that are
generated. This can be changed by clicking Edit by the field’s name.
This page contains the following fields for each log file:
• Log Index—Log entry number.
• Log Time—Time when message was generated.
• Severity—Event severity.
• Description—Message text describing the event.
To clear the messages, click Clear Logs. The messages are cleared.
43 Cisco 300 Series Managed Switches Administration Guide
Page 46
Administration: File Management
This section describes how system files are managed.
The following topics are covered:
• System Files
• Upgrade/Backup Firmware/Language
• Active Image
4
System Files
• Download/Backup Configuration/Log
• Configuration Files Properties
• Copy/Save Configuration
• Auto Configuration/Image Update via DHCP
System files are files that contain configuration information, firmware images or
boot code.
Various actions can be performed with these files, such as: selecting the firmware
file from which the device boots, copying various types of configuration files
internally on the device, or copying files to or from an external device, such as an
external server.
The possible methods of file transfer are:
• Internal copy
• HTTP/HTTPS that uses the facilities that the browser provides
• TFTF/SCP client, requiring a TFTP/SCP server
Cisco 300 Series Managed Switches Administration Guide 44
Page 47
4
Administration: File Management
System Files
Configuration files on the device are defined by their type, and contain the
settings and parameter values for the device.
When a configuration is referenced on the device, it is referenced by its
configuration file type (such as Startup Configuration or Running Configuration),
as opposed to a file name that can be modified by the user.
Content can be copied from one configuration file type to another, but the names
of the file types cannot be changed by the user.
Other files on the device include firmware, boot code, and log files, and are
referred to as operational files.
The configuration files are text files and can be edited in a text editor, such as
Notepad after they are copied to an external device, such as a PC.
Files and File Types
The following types of configuration and operational files are found on the device:
• Running Configuration—Contains the parameters currently being used by
the device to operate. This is the only file type that is modified when you
change parameter values on the device.
If the device is rebooted, the Running Configuration is lost. The Startup
Configuration, stored in Flash, overwrites the Running Configuration, stored
in RAM.
To preserve any changes you made to the device, you must save the
Running Configuration to the Startup Configuration, or another file type.
• Startup Configuration—The parameter values that were saved by copying
another configuration (usually the Running Configuration) to the Startup
Configuration.
The Startup Configuration is retained in Flash and is preserved when the
device is rebooted. At this time, the Startup Configuration is copied to RAM
and identified as the Running Configuration.
• Mirror Configuration—A copy of the Startup Configuration, created by the
device when the following conditions exist:
- The device has been operating continuously for 24 hours.
- No configuration changes have been made to the Running Configuration
in the previous 24 hours.
- The Startup Configuration is identical to the Running Configuration.
45 Cisco 300 Series Managed Switches Administration Guide
Page 48
Administration: File Management
System Files
Only the system can copy the Startup Configuration to the Mirror
Configuration. However, you can copy from the Mirror Configuration to other
file types or to another device.
The option of automatically copying the Running Configuration to the mirror
configuration can be disabled in the Configuration Files Properties page.
• Backup Configuration—A manual copy of a configuration file used for
protection against system shutdown or for the maintenance of a specific
operating state. You can copy the Mirror Configuration, Startup
Configuration, or Running Configuration to a Backup Configuration file. The
Backup Configuration exists in Flash and is preserved if the device is
rebooted.
• Firmware—The program that controls the operations and functionality of
the device. More commonly referred to as the image.
4
• Boot Code—Controls the basic system startup and launches the firmware
image.
• Language File—The dictionary that enables the web-based configuration
utility windows to be displayed in the selected language.
• Flash Log—SYSLOG messages stored in Flash memory.
File Actions
The following actions can be performed to manage firmware and configuration
files:
• Upgrade the firmware or boot code, or replace a second language, as
described in Upgrade/Backup Firmware/Language section.
• View the firmware image currently in use or select the image to be used in
the next reboot as described in the Active Image section.
• Save configuration files on the device to a location on another device as
described in the Download/Backup Configuration/Log section.
• Clear the Startup Configuration or Backup Configuration file types as
described in the Configuration Files Properties section.
• Copy one configuration file type to another configuration file type as
described in the Copy/Save Configuration section.
• Enable automatically uploading a configuration file from a DHCP server to
the device, as described in the section.
Cisco 300 Series Managed Switches Administration Guide 46
Page 49
4
This section covers the following topics:
• Upgrade/Backup Firmware/Language
• Active Image
• Download/Backup Configuration/Log
• Configuration Files Properties
• Copy/Save Configuration
• Auto Configuration/Image Update via DHCP
Upgrade/Backup Firmware/Language
Administration: File Management
Upgrade/Backup Firmware/Language
The Upgrade/Backup Firmware/Language process can be used to:
• Upgrade or backup the firmware image.
• Upgrade or backup the boot code.
• Import or upgrade a second language file.
The following methods for transferring files are supported:
• HTTP/HTTPS that uses the facilities provided by the browser
• TFTP that requires a TFTP server
• Secure Copy Protocol (SCP) that requires an SCP server
If a new language file was loaded onto the device, the new language can be
selected from the drop-down menu. (It is not necessary to reboot the device).
There are two firmware images stored on the device. One of the images is
identified as the active image and other image is identified as the inactive image.
When you upgrade the firmware, the new image always replaces the image
identified as the inactive image.
Even after uploading new firmware on the device, the device continues to boot by
using the active image (the old version) until you change the status of the new
image to be the active image by using the procedure in the Active Image section.
Then boot the device.
47 Cisco 300 Series Managed Switches Administration Guide
Page 50
Administration: File Management
Upgrade/Backup Firmware/Language
Upgrade/Backing Firmware or Language File
To upgrade or backup a software image or language file:
STEP 1 Click Administration > File Management > Upgrade/Backup Firmware/
Language.
STEP 2 Click the Transfer Method. Proceed as follows:
• If you selected TFTP, go to STEP 3.
• If you selected via HTTP/HTTPS, go to STEP 4.
• If you selected via SCP, go to STEP 5.
STEP 3 If you selected via TFTP, enter the parameters as described in this step.
Otherwise, skip to STEP 4.
4
Select one of the following Save Action::
• Upgrade—Specifies that the file type on the device is to be replaced with a
new version of that file type located on a TFTP server.
• Backup—Specifies that a copy of the file type is to be saved to a file on
another device.
Enter the following fields:
• File Type—Select the destination file type. Only valid file types are shown.
(File types are described in the Files and File Types section).
• TFTP Server Definition—Select whether to specify the TFTP server By IP
address or By name.
• IP Version—Select whether an IPv4 or an IPv6 address is used.
• IPv6 Address Type—Select the IPv6 address type (if IPv6 is used). The
options are:
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
Cisco 300 Series Managed Switches Administration Guide 48
Page 51
4
Administration: File Management
Upgrade/Backup Firmware/Language
• Link Local Interface—Select the link local interface (if IPv6 is used) from the
list.
• TFTP Server IP Address/Name—Enter the IP address or the name of the
TFTP server.
• (For Upgrade) Source File Name—Enter the name of the source file.
• (For Backup) Destination File Name—Enter the name of the backup file.
STEP 4 If you selected via HTTP/HTTPS, you can only select the Save Action: Upgrade.
Enter the parameters as described in this step.
• File Type—Select one of the following file types:
- Firmware Image—Select this to upgrade the firmware image.
- Language File—Select this to upgrade the language file.
• File Name—Click Browse to select a file or enter the path and source file
name to be used in the transfer.
STEP 5 If you selected via SCP (Over SSH), see SSH Client Authentication for
instructions. Then, enter the following fields: (only unique fields are described, for
non-unique fields, see the descriptions above)
• Remote SSH Server Authentication—To enable SSH server authentication
(which is disabled by default), click Edit. This takes you to the SSH Server
Authentication page to configure the SSH server, and return to this page.
Use the SSH Server Authentication page to select an SSH user
authentication method (password or public/private key), set a username and
password on the device (if the password method is selected), and generate
an RSA or DSA key if required.
SSH Client Authentication—Client authentication can be done in one of the
following ways:
• Use SSH Client System Credentials—Sets permanent SSH user
credentials. Click System Credentials to go to the SSH User Authentication
page where the user/password can be set once for all future use.
• Use SSH Client One-Time Credentials—Enter the following:
- Username—Enter a username for this copy action.
- Password—Enter a password for this copy.
NOTE The username and password for one-time credential will not saved in
configuration file.
49 Cisco 300 Series Managed Switches Administration Guide
Page 52
Administration: File Management
Upgrade/Backup Firmware/Language
Select one of the following Save Action(s):
• Upgrade—Specifies that the file type on the device is to be replaced with a
new version of that file type located on a TFTP server.
• Backup—Specifies that a copy of the file type is to be saved to a file on
another device.
Enter the following fields:
• File Type—Select the destination file type. Only valid file types are shown.
(The file types are described in the Files and File Types section).
• SCP Server Definition—Select whether to specify the SCP server by IP
address or by domain name.
• IP Version—Select whether an IPv4 or an IPv6 address is used.
• IPv6 Address Type—Select the IPv6 address type (if used). The options
are:
4
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPv6 type that is visible and
reachable from other networks.
• Link Local Interface—Select the link local interface from the list.
• SCP Server IP Address/Name—Enter the IP address or domain name of
the SCP server.
• (For Upgrade) Source File Name—Enter the name of the source file.
• (For Backup) Destination File Name—Enter the name of the backup file.
STEP 6 Click Apply. If the files, passwords and server addresses are correct, one of the
following may happen:
• If SSH server authentication is enabled (in the SSH Server Authentication
page), and the SCP server is trusted, the operation succeeds. If the SCP
server is not trusted, the operation fails and an error is displayed.
Cisco 300 Series Managed Switches Administration Guide 50
Page 53
4
Active Image
Administration: File Management
Active Image
• If SSH server authentication is not enabled, the operation succeeds for any
SCP server.
There are two firmware images stored on the device. One of the images is
identified as the active image and other image is identified as the inactive image.
The device boots from the image you set as the active image. You can change the
image identified as the inactive image to the active image. (You can reboot the
device by using the process described in the Management Interface section).
To select the active image:
STEP 1 Click Administration > File Management > Active Image.
The page displays the following:
• Active Image—Displays the image file that is currently active on the device.
• Active Image Version Number—Displays the firmware version of the active
image.
• Active Image After Reboot—Displays the image that is active after reboot.
• Active Image Version Number After Reboot—Displays the firmware
version of the active image as it be after reboot.
STEP 2 Select the image from the Active Image After Reboot menu to identify the
firmware image that is used as the active image after the device is rebooted. The
Active Image Version Number After Reboot displays the firmware version of the
active image that is used after the device is rebooted.
STEP 3 Click Apply. The active image selection is updated.
Download/Backup Configuration/Log
The Download/Backup Configuration/Log page enables:
• Backing up configuration files or logs from the device to an external device.
51 Cisco 300 Series Managed Switches Administration Guide
Page 54
Administration: File Management
Download/Backup Configuration/Log
• Restoring configuration files from an external device to the device.
When restoring a configuration file to the Running Configuration, the imported file
adds any configuration commands that did not exist in the old file and overwrites
any parameter values in the existing configuration commands.
When restoring a configuration file to the Startup Configuration or a backup
configuration file, the new file replaces the previous file.
When restoring to Startup Configuration, the device must be rebooted for the
restored Startup Configuration to be used as the Running Configuration. You can
reboot the device by using the process described in the Management Interface
section.
Configuration File Backwards Compatibility
4
When restoring configuration files from an external device to the device, the
following compatibility issues might arise:
• Change the System Mode—If the System mode is contained in a
configuration file that is downloaded to the device, and the file's System
mode matches the current System mode, this information is ignored.
Otherwise, if the System mode is changed, the following cases are
possible:
- If the configuration file is downloaded onto the device (using the
Download/Backup Configuration/Log page), the operation is aborted,
and a message is displayed indicating that the System mode must be
changed in the System Settings page.
- If the configuration file is downloaded during an automatic configuration
process, the Startup Configuration file is deleted and the device reboots
automatically in the new System mode. The device is configured with an
empty configuration file.
Downloading or Backing-up a Configuration or Log File
To backup or restore the system configuration file:
STEP 1 Click Administration > File Management > Download/Backup Configuration/
Log.
STEP 2 Select the Transfer Method.
Cisco 300 Series Managed Switches Administration Guide 52
Page 55
4
Administration: File Management
Download/Backup Configuration/Log
STEP 3 If you selected via TFTP, enter the parameters. Otherwise, skip to STEP 4.
Select either Download or Backup as the Save Action.
Download—Specifies that the file on another device replaces a file type on the
device. Enter the following fields:
a. TFTP Server Definition—Select whether to specify the TFTP server by IP
address or by domain name.
b. IP Version—Select whether an IPv4 or an IPv6 address is used.
NOTE If the server is selected by name in the Server Definition, there is no
need to select the IP Version related options.
c. IPv6 Address Type—Select the IPv6 address type (if used). The options are:
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
d. Link Local Interface—Select the link local interface from the list.
e. TFTP Server IP Address/Name—Enter the IP address or name of the TFTP
server.
f. Source File Name—Enter the source file name. File names cannot contain
slashes (\ or /), cannot start with a period (.), and must include between 1 and
160 characters. (Valid characters: A-Z, a-z, 0-9, “.”, “-”, “_”).
g. Destination File Type—Enter the destination configuration file type. Only valid
file types are displayed. (The file types are described in the Files and File
Types section).
Backup—Specifies that a file type is to be copied to a file on another device. Enter
the following fields:
a. TFTP Server Definition—Select whether to specify the TFTP server by IP
address or by domain name.
b. IP Version—Select whether an IPv4 or an IPv6 address is used.
c. IPv6 Address Type—Select the IPv6 address type (if used). The options are:
53 Cisco 300 Series Managed Switches Administration Guide
Page 56
Administration: File Management
Download/Backup Configuration/Log
• Link Local—The IPv6 address uniquely identifies hosts on a single network
link. A link local address has a prefix of FE80, is not routable, and can be used
for communication only on the local network. Only one link local address is
supported. If a link local address exists on the interface, this entry replaces
the address in the configuration.
• Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
d. Link Local Interface—Select the link local interface from the list.
e. TFTP Server IP Address/Name—Enter the IP address or name of the TFTP
server.
f. Source File Type—Enter the source configuration file type. Only valid file
types are displayed. (The file types are described in the Files and File Types
section).
4
g. Sensitive Data—Select how sensitive data should be included in the backup
file. The following options are available:
- Exclude—Do not include sensitive data in the backup.
- Encrypted—Include sensitive data in the backup in its encrypted form.
- Plaintext—Include sensitive data in the backup in its plaintext form.
NOTE The available sensitive data options are determined by the current
user SSD rules. For details, refer to Secure Sensitive Data Management >
SSD Rules page.
h. Destination File Name—Enter the destination file name. File names cannot
contain slashes (\ or /), the leading letter of the file name must not be a period
(.), and the file name must be between 1 and 160 characters. (Valid characters:
A-Z, a-z, 0-9, “.”, “-”, “_”).
i. Click Apply. The file is upgraded or backed up.
Cisco 300 Series Managed Switches Administration Guide 54
Page 57
4
Administration: File Management
Download/Backup Configuration/Log
STEP 4 If you selected via HTTP/HTTPS, enter the parameters as described in this step.
Select the Save Action.
If Save Action is Download (replacing the file on the device with a new version
from another device), do the following. Otherwise, go to the next procedure in this
step.
a. Source File Name—Click Browse to select a file or enter the path and source
file name to be used in the transfer.
b. Destination File Type—Select the configuration file type. Only valid file types
are displayed. (The file types are described in the Files and File Types
section).
c. Click Apply. The file is transferred from the other device to the device.
If Save Action is Backup (copying a file to another device), do the following:
a. Source File Type—Select the configuration file type. Only valid file types are
displayed. (The file types are described in the Files and File Types section).
b. Sensitive Data—Select how sensitive data should be included in the backup
file. The following options are available:
- Exclude—Do not include sensitive data in the backup.
- Encrypted—Include sensitive data in the backup in its encrypted form.
- Plaintext—Include sensitive data in the backup in its plaintext form.
NOTE The available sensitive data options are determined by the current
user SSD rules. For details, refer to Secure Sensitive Data Management >
SSD Rules page.
c. Click Apply. The file is upgraded or backed up.
STEP 5 If you selected via SCP (Over SSH), see SSH Client Configuration Through the
GUI for instructions. Then enter the following fields:
• Remote SSH Server Authentication—To enable SSH server authentication
(it is disabled by default), click Edit, which takes you to the SSH Server
Authentication page to configure this, and return to this page. Use the SSH
Server Authentication page to select an SSH user authentication method
(password or public/private key), set a username and password on the
device, if the password method is selected, and generate an RSA or DSA
key if required.
55 Cisco 300 Series Managed Switches Administration Guide
Page 58
Administration: File Management
Download/Backup Configuration/Log
SSH Client Authentication—Client authentication can be done in one of the
following ways:
• Use SSH Client System Credentials—Sets permanent SSH user
credentials. Click System Credentials to go to the SSH User Authentication
page where the user/password can be set once for all future use.
• Use SSH Client One-Time Credentials—Enter the following:
- Username—Enter a username for this copy action.
- Password—Enter a password for this copy.
• Save Action—Select whether to backup or restore the system configuration
file.
• SCP Server Definition—Select whether to specify the SCP server by IP
address or by domain name.
4
• IP Version—Select whether an IPv4 or an IPv6 address is used.
• IPv6 Address Type—Select the IPv6 address type (if used). The options
are:
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
• Link Local Interface—Select the link local interface from the list.
• SCP Server IP Address/Name—Enter the IP address or name of the SCP
server.
If Save Action is Download (replacing the file on the device with a new version
from another device), enter the following fields.
• Source File Name—Enter the name of the source file.
• Destination File Type—Select the configuration file type. Only valid file
types are displayed. (The file types are described in the Files and File
Types section).
Cisco 300 Series Managed Switches Administration Guide 56
Page 59
4
Administration: File Management
Configuration Files Properties
If Save Action is Backup (copying a file to another device), enter the following
fields (in addition to those fields listed above):
• Source File Type—Select the configuration file type. Only valid file types
are displayed. (The file types are described in the Files and File Types
section).
• Sensitive Data—Select how sensitive data should be included in the
backup file. The following options are available:
- Exclude—Do not include sensitive data in the backup.
- Encrypted—Include sensitive data in the backup in its encrypted form.
- Plaintext—Include sensitive data in the backup in its plaintext form.
NOTE The available sensitive data options are determined by the current
user SSD rules. For details, refer to Secure Sensitive Data Management >
SSD Rules page.
• Destination File Name—Name of file being copied to.
STEP 6 Click Apply. The file is upgraded or backed up.
Configuration Files Properties
The Configuration Files Properties page displays when various system
configuration files were created. It also enables deleting the Startup Configuration
and Backup Configuration files. You cannot delete the other configuration file
types.
To set whether mirror configuration files will be created, clear configuration files
and see when configuration files were created:
STEP 1 Click Administration > File Management > Configuration Files Properties.
This page displays the following fields:
• Configuration File Name—Type of system file.
• Creation Time—Date and time that file was modified.
STEP 2 If required, disable Auto Mirror Configuration. This disables the automatic
creation of mirror configuration files. When disabling this feature, the mirror
57 Cisco 300 Series Managed Switches Administration Guide
Page 60
Administration: File Management
!
Copy/Save Configuration
configuration file, if it exists, is deleted. See System Files for a description of
mirror files and why you might not want to automatically create mirror
configuration files.
STEP 3 If required, select either the Startup Configuration, Backup Configuration or both
and click Clear Files to delete these files.
Copy/Save Configuration
When you click Apply on any window, changes that you made to the device
configuration settings are stored only in the Running Configuration. To preserve
the parameters in the Running Configuration, the Running Configuration must be
copied to another configuration type or saved on another device.
4
CAUTION Unless the Running Configuration is copied to the Startup Configuration or another
configuration file, all changes made since the last time the file was copied are lost
when the device is rebooted.
The following combinations of copying internal file types are allowed:
• From the Running Configuration to the Startup Configuration or Backup
Configuration.
• From the Startup Configuration to the Running Configuration, Startup
Configuration or Backup Configuration.
• From the Backup Configuration to the Running Configuration, Startup
Configuration or Backup Configuration.
• From the Mirror Configuration to the Running Configuration, Startup
Configuration or Backup Configuration.
To copy one type of configuration file to another type of configuration file:
STEP 1 Click Administration > File Management > Copy/Save Configuration.
STEP 2 Select the Source File Name to be copied. Only valid file types are displayed
(described in the Files and File Types section).
STEP 3 Select the Destination File Name to be overwritten by the source file.
Cisco 300 Series Managed Switches Administration Guide 58
Page 61
4
Administration: File Management
Auto Configuration/Image Update via DHCP
STEP 4 Select the Sensitive Data option if you are backing up a configuration file, select
one of the following formats for the backup file.
- Exclude—Sensitive data is not included in the backup file.
- Encrypted—Sensitive data is included in the backup file in encrypted
form.
- Plaintext—Sensitive data is included in the backup file in plain text.
NOTE The available sensitive data options are determined by the current
user SSD rules. For details, refer to Secure Sensitive Data Management >
SSD Rules page.
STEP 5 The Save Icon Blinking field indicates whether an icon blinks when there is
unsaved data. To disable/enable this feature, click Disable/Enable Save Icon
Blinking.
STEP 6 Click Apply. The file is copied.
Auto Configuration/Image Update via DHCP
The Auto Configuration/Image Update feature provides a convenient method to
automatically configure Cisco 200, 300 and 500 switches in a network and
upgrade their firmware. This process enables the administrator to remotely ensure
that the configuration and firmware of these devices in the network are up-to-date.
This feature is comprised of the following parts:
• Auto Image Update—Automatic downloading a firmware image from a
remote TFTP/SCP server. At the end of the Auto Configuration/Image
Update process, the device reboots itself to the firmware image.
• Auto Configuration—Automatic downloading a configuration file from a
remote TFTP/SCP server. At the end of the Auto Configuration/Image
process, the device reboots itself to the configuration file.
NOTE If both Auto Image Update and Auto Configuration are requested, Auto Image
Update is performed first, then after reboot, Auto Configuration is performed and
then a final reboot is performed.
59 Cisco 300 Series Managed Switches Administration Guide
Page 62
Administration: File Management
Auto Configuration/Image Update via DHCP
To use this feature, configure a DHCP server in the network with the locations and
names of the configuration file and firmware image of your devices. The devices in
the network are configured as DHCP clients by default. When the devices are
assigned their IP addresses by the DHCP server, they also receive information
about the configuration file and firmware image. If the configuration file and/or
firmware image are different from the ones currently used on the device, the
device reboots itself after downloading the file and/or image. This section
describes these processes.
In addition to the ability to keep the devices in the network updated with the latest
configuration files and firmware image, Auto-Update/Configuration enables quick
installation of new devices on the network, since an out-of-the-box device is
configured to retrieve its configuration file and software image from the network
without any manual intervention by the system administrator. The first time that it
applies for its IP address from the DHCP server, the device downloads and
reboots itself with the configuration file and/or image specified by the DHCP
server.
4
The Auto Configuration process supports downloading a configuration file that
includes sensitive information, such as RADIUS server keys and SSH/SSL keys, by
using the Secured Copy Protocol (SCP) and the Secure Sensitive Data (SSD)
feature (See SSH Client Authentication and Security: Secure Sensitive Data
Management).
Download Protocols (TFTP or SCP)
Configuration files and firmware images can be downloaded from either a TFTP or
an SCP server.
The user configures the protocol to be used, as follows:
• Auto By File Extension—(Default) If this option is selected, a user-defined
file extension indicates that files with this extension are downloaded using
SCP (over SSH), while files with other extensions are downloaded using
TFTP. For example, if the file extension specified is.xyz, files with the .xyz
extension are downloaded using SCP, and files with the other extensions
are downloaded using TFTP. The default extension is .scp.
• TFTP Only—The download is done through TFTP, regardless of the file
extension of the configuration file name.
• SCP Only—The download is done through SCP (over SSH), regardless of
the file extension of the configuration file name.
Cisco 300 Series Managed Switches Administration Guide 60
Page 63
4
Administration: File Management
Auto Configuration/Image Update via DHCP
SSH Client Authentication
SCP is SSH based. By default, remote SSH server authentication is disabled, so
that the device accepts any remote SSH server out of the box. You can enable
remote SSH server authentication so that only servers found in the trusted server
list can be used.
SSH client authentication parameters are required to access the SSH server by
the client (which is the device). The default SSH client authentication parameters
are:
• SSH authentication method: by username/password
• SSH username: anonymous
• SSH password: anonymous
NOTE The SSH client authentication parameters can also be used when downloading a
file manually (meaning, a download that is not performed through the DHCP Auto
Configuration/Image Update feature).
Auto Configuration/Image Update Process
DHCP Auto Configuration uses the configuration server name/address and
configuration file name/path, if any, in the DHCP messages received. In addition,
DHCP Image Update uses the indirect file name of the firmware, if any, in the
messages. This information is specified as DHCP options in the Offer message
coming from the DHCPv4 servers and in the Information Reply messages coming
from DHCPv6 servers.
If this information is not found in the DHCP server messages, backup information
that has been configured in the DHCP Auto Configuration/Image Update page is
used.
When the Auto Configuration/Image Update process is triggered (see Auto
Configuration/Image Update Trigger), the sequence of events described below
occurs.
Auto Image Update Starts:
• The switch uses the indirect file name from option 125 (DHCPv4) and option
60 (DHCPv6) if any, from the DHCP message received.
• If the DHCP server did not send the indirect file name of the firmware image
file, the Backup Indirect Image File Name (from the DHCP Auto
Configuration/Image Update page) is used.
61 Cisco 300 Series Managed Switches Administration Guide
Page 64
Administration: File Management
Auto Configuration/Image Update via DHCP
• The switch downloads the Indirect Image File and extracts from it the name
of the TFTP/SCP server's image file.
• The switch compares the version of the TFTP server's image file with the
version of the switch active image.
• If the two versions are different, the new version is loaded into the non-
active image, a reboot is performed and the non-active image becomes the
active image.
• When using the SCP protocol, a SYSLOG message is generated informing
that reboot is about to start.
• When using the SCP protocol, a SYSLOG message is generated
acknowledging that the Auto Update process is completed.
• When using the TFTP protocol, SYSLOG messages are generated by the
copy process.
4
Auto Configuration Starts:
• The device uses the TFTP/SCP server name/address and configuration file
name/path (DHCPv4 options: 66,150, and 67, DHCPv6 options: 59 and 60), if
any, from the DHCP message received.
• If the information is not sent by the DHCP server, the Backup Server IP
Address/Name and the Backup Configuration File Name (from the DHCP
Auto Configuration/Image Update page) is used.
• The new configuration file is used if its name is different than the name of
the configuration file previously used on the device or if the device has
never been configured.
• The device is rebooted with the new configuration file, at the end of the
Auto Configuration/Image Update Process.
• SYSLOG messages are generated by the copy process.
Missing Options
• If the DHCP server did not send the TFTP/SCP server address in a DHCP
option and the backup TFTP/SCP server address parameter has not been
configured, then:
- SCP—The Auto Configuration process is halted.
- TFTP—The device sends TFTP Request messages to a limited
Broadcast address (for IPv4) or ALL NODES address (for IPv6) on its IP
Cisco 300 Series Managed Switches Administration Guide 62
Page 65
4
Administration: File Management
Auto Configuration/Image Update via DHCP
interfaces and continues the process of Auto Configuration/Image
Update with the first answering TFTP server.
Download Protocol Selection
• The copy protocol (SCP/TFTP) is selected, as described in Download
Protocols (TFTP or SCP).
SCP
• When downloading using SCP, the device accepts any specified SCP/SSH
server (without authentication) if either of the following is true:
- The SSH server authentication process is disabled. By default the SSH
server authentication is disabled in order to allow downloading
configuration file for devices with factory default configuration (for
example out-of-box devices).
- The SSH Server is configured in the SSH Trusted Servers list.
If the SSH server authentication process is enabled, and the SSH server is
not found in the SSH Trusted Servers list, the Auto Configuration process is
halted.
• If the information is available, the SCP server is accessed to download the
configuration file or image from it.
Auto Configuration/Image Update Trigger
Auto Configuration/Image Update via DHCPv4 is triggered when the following
conditions are fulfilled:
• The IP address of the device is dynamically assigned/renewed at reboot, or
explicitly renewed by administrative action, or automatically renewed due
to an expiring lease. Explicit renewal can be activated in the IPv4 Interface
page.
• If Auto Image Update is enabled, the Auto Image Update process is
triggered when an indirect image file name is received from a DHCP server
or a backup indirect image file name has been configured. Indirect means
that this is not the image itself, but rather a file that holds the path name to
the image.
• If Auto Configuration is enabled, the Auto Configuration process is triggered
when the configuration file name is received from a DHCP server or a
backup configuration file name has been configured.
63 Cisco 300 Series Managed Switches Administration Guide
Page 66
Administration: File Management
Auto Configuration/Image Update via DHCP
Auto Configuration/Image Update via DHCPv6 is triggered when the following
conditions are fulfilled:
• When a DHCPv6 server sends information to the device. This occurs in the
following cases:
- When an IPv6-enabled interface is defined as a DHCPv6 stateless
configuration client.
- When DHCPv6 messages are received from the server (for example,
when you press the Restart button on IPv6 Interfaces page,
- When DHCPv6 information is refreshed by the device.
- After rebooting the device when stateless DHCPv6 client is enabled.
• When the DHCPv6 server packets contain the configuration filename
option.
4
• The Auto Image Update process is triggered when an indirect image file
name is provided by the DHCP server or a backup indirect image file name
has been configured. Indirect means that this is not the image itself, but
rather a file that holds the path name to the image.
Ensuring Correct Performance
To ensure that the Auto Configuration/Image Update feature works correctly, note
the following:
• A configuration file that is placed on the TFTP/SCP server must match the
form and format requirements of the supported configuration file. The form
and format of the file are checked, but the validity of the configuration
parameters is not checked prior to loading it to the Startup Configuration.
• In IPv4, to ensure that a device downloads the configuration and images file
as intended during the Auto Configuration/Image Update process, it is
recommended that the device is always assigned the same IP address.
This ensures that the device is always assigned with the same IP address,
and obtains the same information used in Auto Configuration/Image Update.
DHCP Auto Configuration/Image Update
The following GUI pages are used to configure the device:
• Administration > File Management > DHCP Auto Configuration/Image
Update—To configure the device as a DHCP client.
Cisco 300 Series Managed Switches Administration Guide 64
Page 67
4
Administration: File Management
Auto Configuration/Image Update via DHCP
• Administration > Management Interface > IPv4 Interface (In L2) or IP
Configuration > IPv4 Management and Interfaces > IPv4 Interfaces (in L3)—
To renew the IP address through DHCP when the device is in Layer 2
system mode.
Default Settings and Configuration
The following defaults exist on the system:
• Auto Configuration is enabled.
• Auto Image Update is enabled.
• The device is enabled as a DHCP client.
• Remote SSH server authentication is disabled.
Before You Start the Auto Configuration/Image Update Process
To use this feature, the device must either be configured as a DHCPv4 or DHCPv6
client. The type of DHCP client defined on the device is in correlation with the type
of interfaces defined on the device.
Auto Configuration Preparations on the Server
To prepare the DHCP and TFTP/SCP servers, do the following:
TFTP/SCP Server
• Place a configuration file in the working directory. This file can be created
by copying a configuration file from a device. When the device is booted,
this becomes the Running Configuration file.
DHCP Server
Configure the DHCP server with the following options:
• DHCPv4:
- 66 (single server address) or 150 (list of server addresses)
- 67 (name of configuration file)
• DHCPv6
- Option 59 (server address)
65 Cisco 300 Series Managed Switches Administration Guide
Page 68
Administration: File Management
Auto Configuration/Image Update via DHCP
- Options 60 (name of configuration file plus indirect image file name,
separated by a comma)
Auto Image Update Preparations
To prepare the DHCP and TFTP/SCP servers do the following:
TFTP/SCP Server
1. Create a sub directory in the main directory. Place a software image file in it.
2. Create an indirect file that contains a path and the name of the firmware version
(for example indirect-cisco.txt that contains cisco\cisco-version.ros).
3. Copy this indirect file to the TFTP/SCP server’s main directory
DHCP Server
4
Configure the DHCP server with the following options
• DHCPv4—Option 125 (indirect file name)
• DHCPv6—Options 60 (name of configuration file plus indirect image file
name, separated by a comma)
DHCP Client Work Flow
STEP 1 Configure Auto Configuration and/or Auto Image Update parameters in the
Administration > File Management > DHCP Auto Configuration/Image Update
page.
STEP 2 Set the IP Address Type to Dynamic in the Defining an IPv4 Interface in Layer 2
System Mode or Defining IPv4 Interface in Layer 3 System Mode pages, and/
or define the device as a stateless DHCPv6 client in the IPv6 Interface page.
Web Configuration
To configure Auto Configuration and/or Auto Update:
STEP 1 Click Administration > File Management > DHCP Auto Configuration/Image
Update.
STEP 2 Enter the values.
• Auto Configuration Via DHCP—Select this field to enable DHCP Auto
Configuration. This feature is enabled by default, but can be disabled here.
Cisco 300 Series Managed Switches Administration Guide 66
Page 69
4
Administration: File Management
Auto Configuration/Image Update via DHCP
• Download Protocol—Select one of the following options:
Auto By File Extension
-
the TFTP or SCP protocol depending on the extension of the
configuration file. If this option is selected, the extension of the
configuration file does not necessarily have to be given. If it is not given,
the default extension is used (as indicated below).
-
File Extension for SCP
indicate a file extension here. Any file with this extension is downloaded
using SCP. If no extension is entered, the default file extension .scp is
used.
-
TFTP Only
for auto configuration.
SCP Only
-
auto configuration.
• Image Auto Update Via DHCP—Select this field to enable update of the
firmware image from the DHCP server. This feature is enabled by default, but
can be disabled here.
• Download Protocol—Select one of the following options:
—Select to indicate that only the TFTP protocol is to be used
—Select to indicate that only the SCP protocol is to be used for
—Select to indicate that Auto Configuration uses
—If Auto By File Extension is selected, you can
Auto By File Extension
-
TFTP or SCP protocol depending on the extension of the image file. If this
option is selected, the extension of the image file does not necessarily
have to be given. If it is not given, the default extension is used (as
indicated below).
-
File Extension for SCP
indicate a file extension here. Any file with this extension is downloaded
using SCP. If no extension is entered, the default file extension .scp is
used.
-
TFTP Only
for auto update.
SCP Only
-
auto update.
• SSH Settings for SCP—When using SCP for downloading the configuration
files, select one of the following options:
—Select to indicate that only the TFTP protocol is to be used
—Select to indicate that only the SCP protocol is to be used for
—Select to indicate that auto update uses the
—If Auto By File Extension is selected, you can
67 Cisco 300 Series Managed Switches Administration Guide
Page 70
Administration: File Management
Auto Configuration/Image Update via DHCP
• Remote SSH Server Authentication—Click on the Enable/Disable link to
navigate to the SSH Server Authentication page. There you can enable
authentication of the SSH server to be used for the download and enter the
trusted SSH server if required.
• SSH Client Authentication—Click on the System Credentials link to enter
user credentials in the SSH User Authentication page.
• Backup Server Definition—Select whether the backup server will be
configured By IP address or By name.
• IP Version—Select whether an IPv4 or an IPv6 address is used.
• IPv6 Address Type—Select the IPv6 address type (if IPv6 is used). The
options are:
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
4
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
• Link Local Interface—Select the link local interface (if IPv6 is used) from the
list.
STEP 3 Enter the following optional information that is used if the DHCP server did not
provide the required information.
• Backup Server IP Address/Name—Enter either the backup server IP
address or name.
• Backup Configuration File Name—Enter the backup configuration file
name.
• Backup Indirect Image File Name—Enter the indirect image file name to
be used. This is
indirect image file name is: indirect-cisco.scp. This file contains the path and
name of the firmware image.
The following fields are displayed:
• Last Auto Configuration/Image Server IP Address—Address of the last
backup server.
a file that holds the path to the image. An example of an
Cisco 300 Series Managed Switches Administration Guide 68
Page 71
4
Administration: File Management
• Last Auto Configuration File Name—Name of the last configuration file
name.
STEP 4 Click Apply. The parameters are copied to the Running Configuration file.
69 Cisco 300 Series Managed Switches Administration Guide
Page 72
Administration: File Management
4
Cisco 300 Series Managed Switches Administration Guide 70
Page 73
4
Administration: File Management
71 Cisco 300 Series Managed Switches Administration Guide
Page 74
Administration
This section describes how to view system information and configure various
options on the device.
It covers the following topics:
• Device Models
• System Settings
5
• Console Settings (Autobaud Rate Support)
• Management Interface
• User Accounts
• Defining Idle Session Timeout
• Time Settings
• System Log
• File Management
• Rebooting the Device
• Routing Resources
• Health
• Diagnostics
• Discovery - Bonjour
• Discovery - LLDP
• Discovery - CDP
• Ping
• Traceroute
Cisco 300 Series Managed Switches Administration Guide 72
Page 75
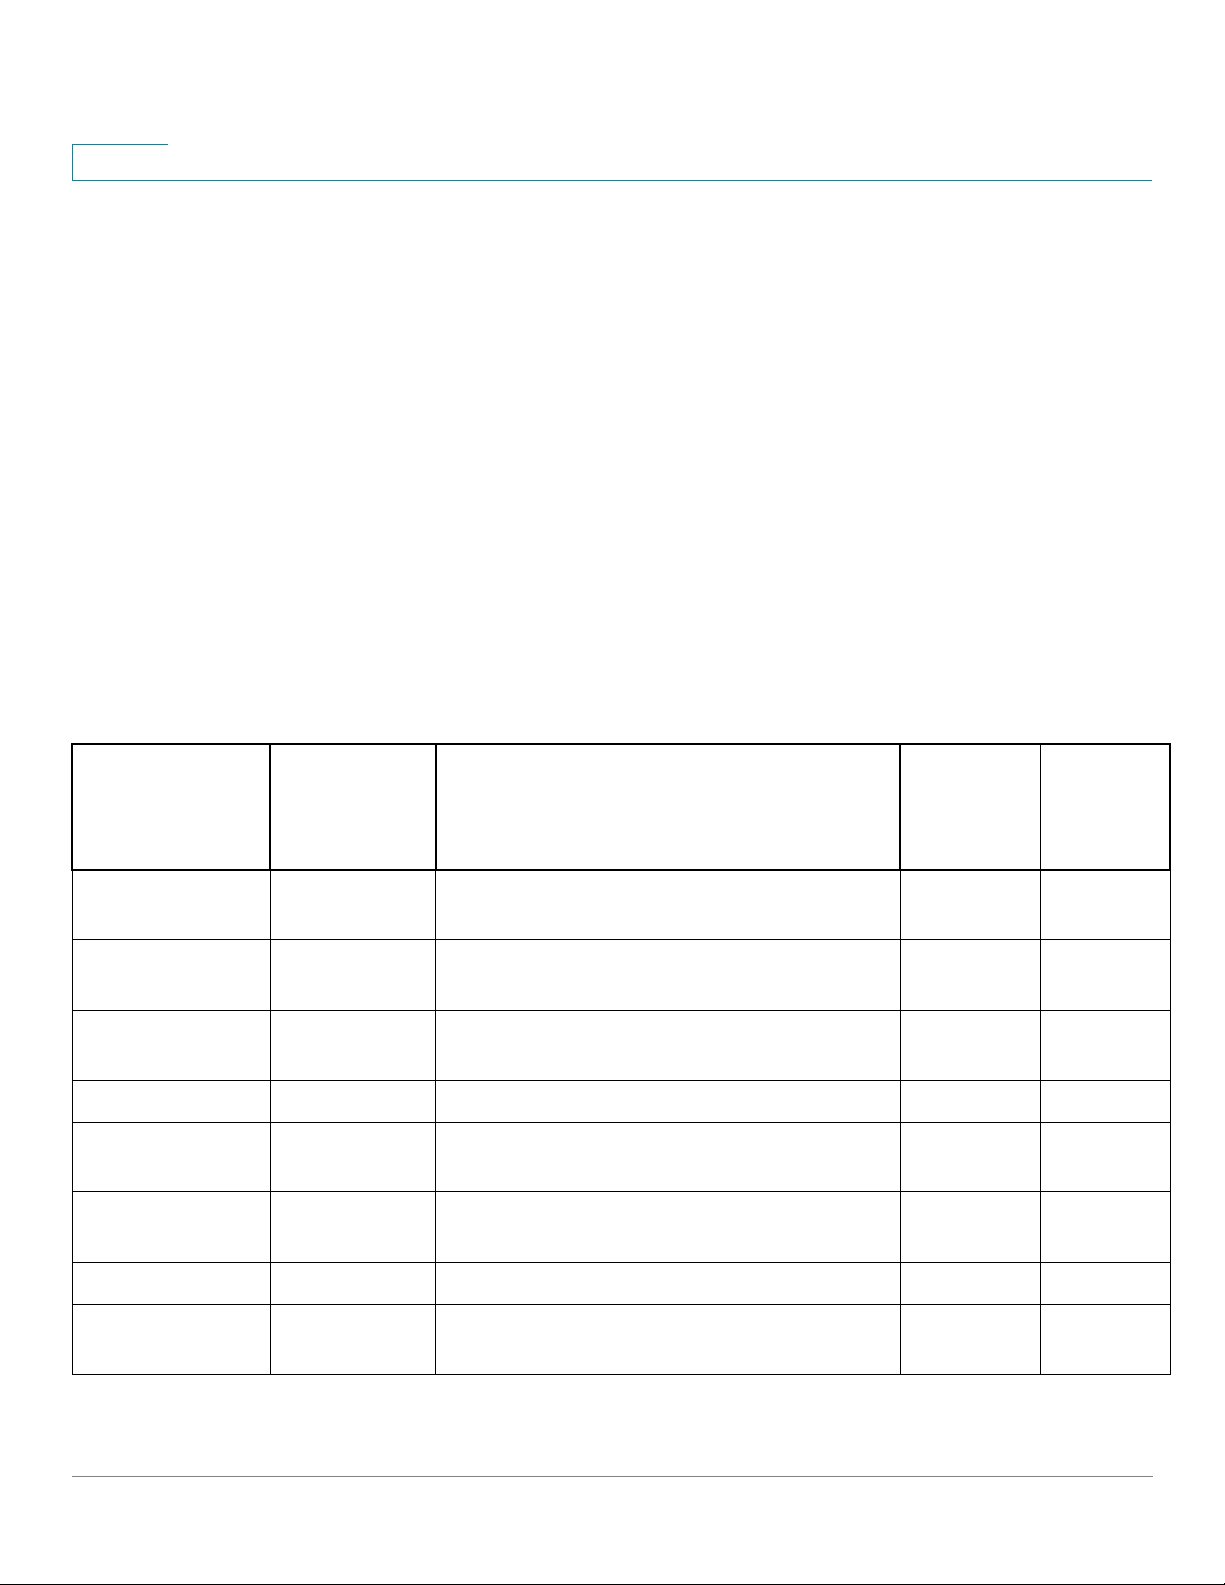
5
Device Models
NOTE See Interface Naming Conventions for port naming conventions.
Administration
Device Models
All models can be fully managed through the web-based switch configuration
utility.
In Layer 2 system mode, the device acts as a VLAN-aware bridge and forwards
packets. In Layer 3 system mode, the device performs both IPv4 routing and
VLAN-aware bridging.
When the device operates in Layer 3 system mode, the VLAN Rate Limit, and QoS
policers are not operational. Other QoS Advanced mode features are operational.
The following table describes the various models, the number and type of ports
on them and their PoE information.
Model Name Product ID
(PID)
SG300-28 SRW2024-K9 24 GE ports, and 4 special-purpose ports -
SG300-28P SRW2024P-K924 GE ports, and 4 special-purpose ports -
SG300-52 SRW2048-K9 48 GE ports, and 4 special-purpose ports -
SF300-08 SRW208-K9 8 FE ports. N/A N/A
SF302-08 SRW208G-
K9
SF302-08MP SRW208MP-K98 FE ports plus 2 GE ports 124W 8
Description of Ports on Device Power
Dedicated
to PoE
N/A N/A
2 uplinks and 2 combo-ports
180W 24
2 uplinks and 2 combo-ports.
N/A N/A
2 uplinks and 2 combo-ports
8 FE ports plus 2 GE ports N/A N/A
No. of
Ports that
Support
PoE
SF302-08P SRW208P-K9 8 FE ports plus 2 GE ports 62W 8
SF300-24 SRW224G4-K924 FE ports plus 4 GE special-purpose
ports - 2 uplinks and 2 combo-ports.
73 Cisco 300 Series Managed Switches Administration Guide
N/A N/A
Page 76
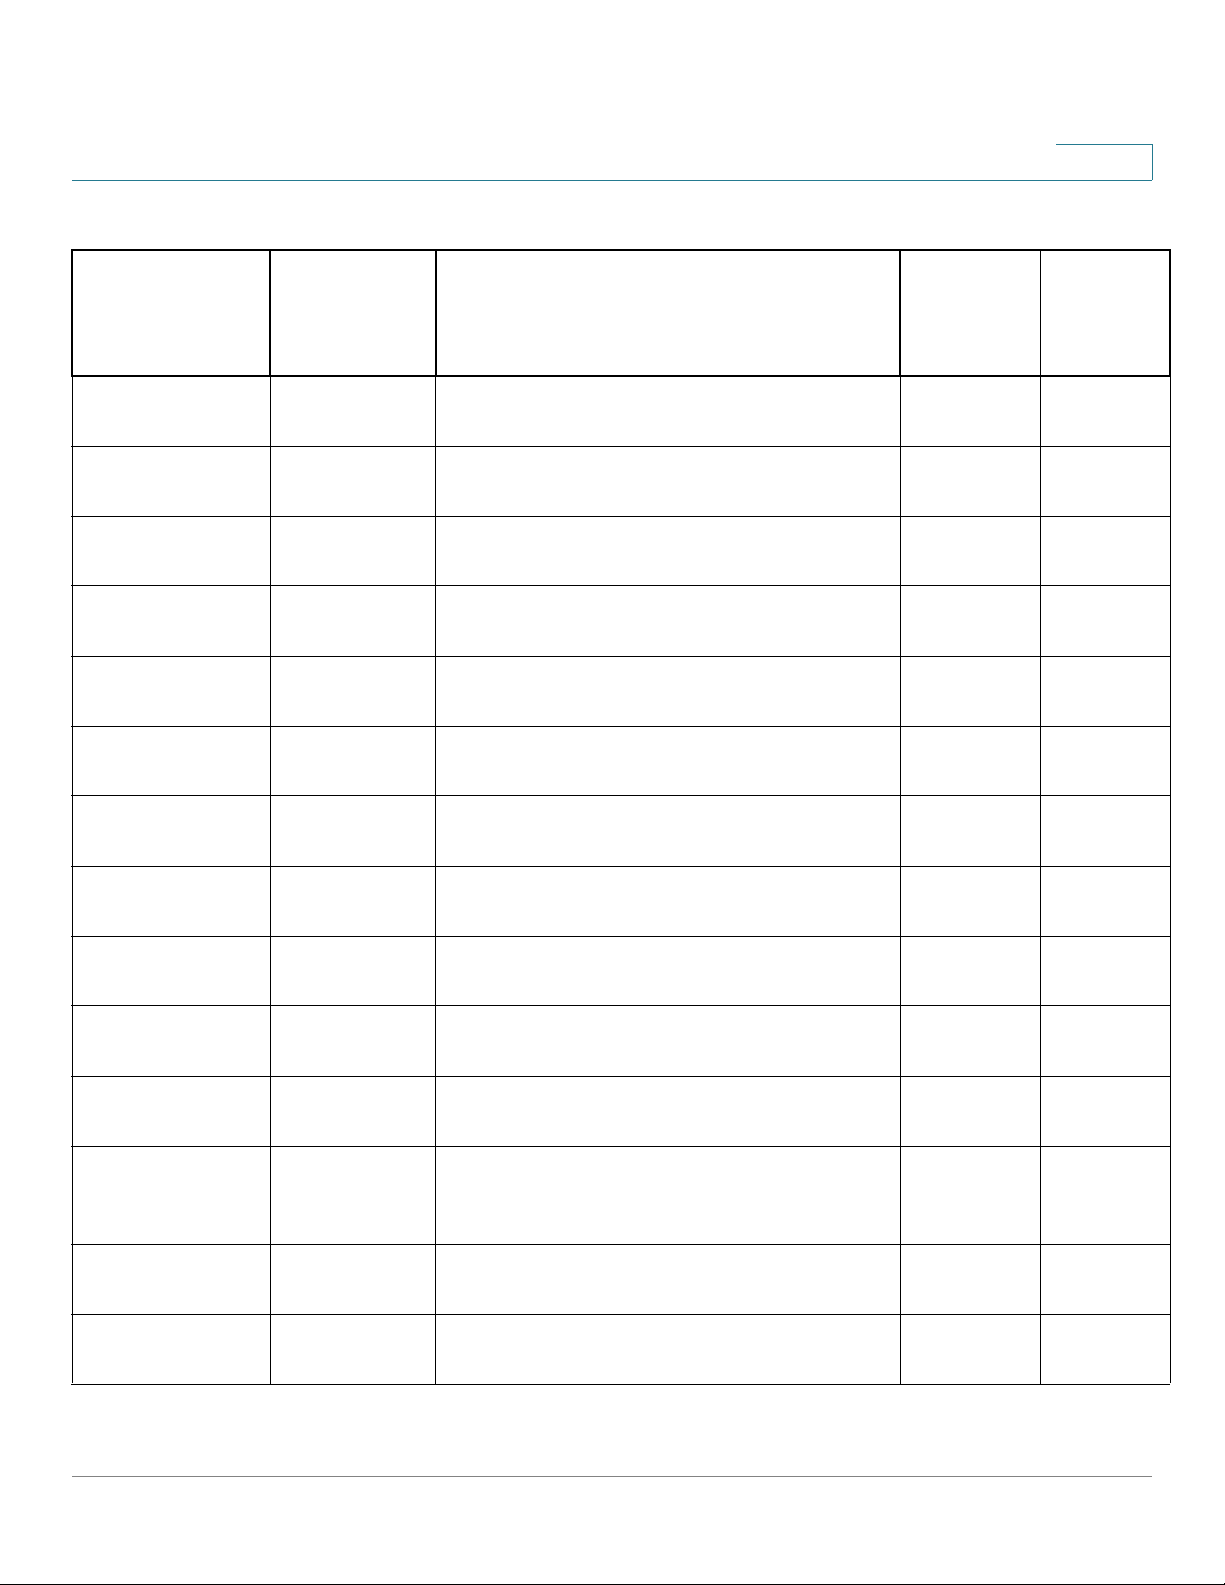
Administration
Device Models
5
Model Name Product ID
(PID)
SF300-24P SRW224G4P
-K9
SF300-48 SRW248G4-K948 FE ports plus 4 GE special-purpose
SF300-48P SRW248G4P
-K9
SF300-24MP SF300-24M-K924-Port 10/100 PoE Managed Switch 375W 24
SG300-28MP SRW2024P-K928-Port Gigabit PoE Managed Switch 375W 24
SG300-52P SG300-52P-
K9 V.0
SG300-52MP SG300-
52MP-K9
Description of Ports on Device Power
Dedicated
to PoE
24 FE ports plus 4 GE special-purpose
ports - 2 uplinks and 2 combo-ports.
ports - 2 uplinks and 2 combo-ports
48 FE ports plus 4 GE special-purpose
ports - 2 uplinks and 2 combo-ports
52-Port Gigabit PoE Managed Switch 375W 48 PoE
52-Port Gigabit PoE Managed Switch 740W 48
180W 24
N/A N/A
375W 48
No. of
Ports that
Support
PoE
ports
SG300-10SFP SG300-
10SFP-K9
ESW2-350G-52 ESW2-350G-
52-K9
ESW2-350G52DC
SF302-08PP SF302-08PP-
SF302-08MPP SF302-
SG300-10PP SG300-10PP-K98-Port 10/100 PoE Managed Switch 62W 8
SG300-10MPP SG300-
ESW2-350G52DC-K9
K9 V.0
08MPP-K9
V. 0
10MPP-K9
10-Port Gigabit Managed SFP Switch N/A N/A
52-Port Gigabit Managed Switch N/A N/A
52-Port Gigabit Managed Switch N/A N/A
8-Port 10/100 PoE Managed Switch 62W 8
8-Port 10/100 PoE Managed Switch 124W 8
10-Port Gigabit PoE Managed Switch 124W 8
Cisco 300 Series Managed Switches Administration Guide 74
Page 77
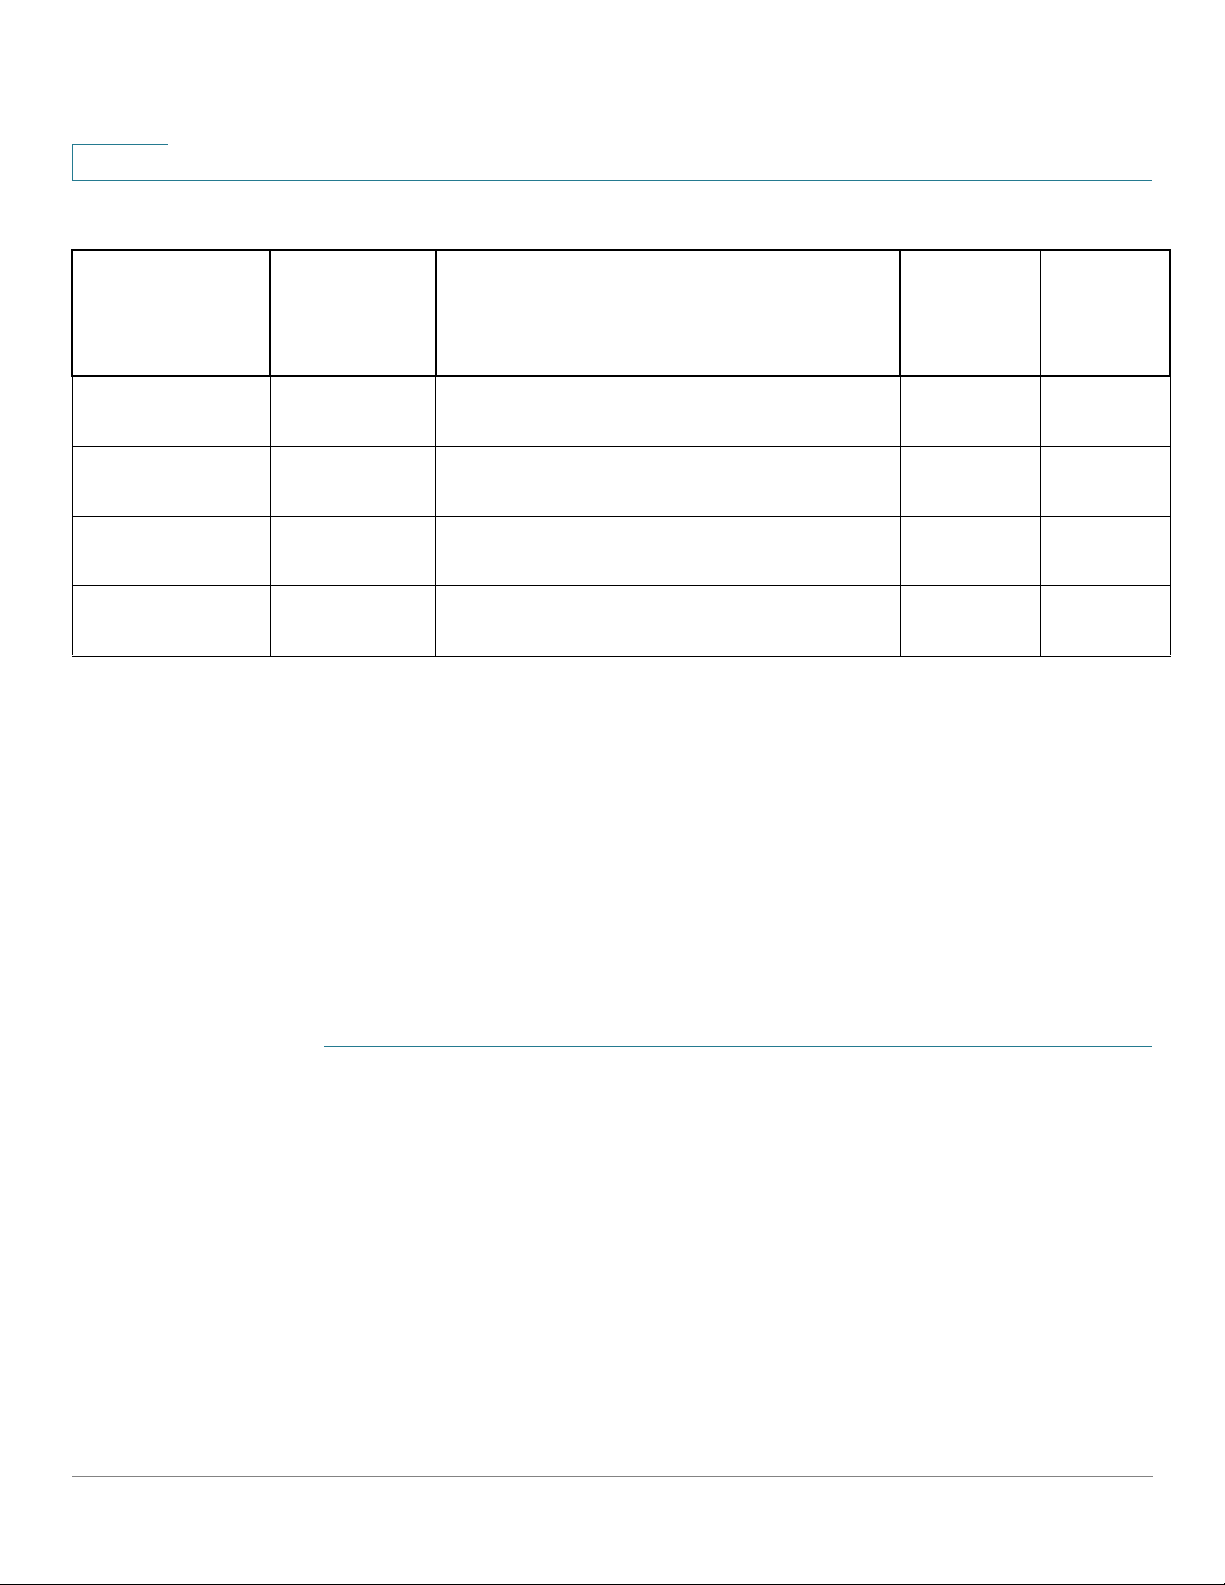
5
Administration
System Settings
Model Name Product ID
(PID)
SF300-24PP SF300-24PP-K924-Port 10/100 PoE Managed Switch 180W 24
SF300-24PP SF300-24PP-K924-Port 10/100 PoE Managed Switch 180W 24
SF300-48PP SF300-48PP-K948-Port 10/100 PoE Managed Switch 375W 48
SG300-28SFP SG300-
28SFP-K9
Description of Ports on Device Power
Dedicated
to PoE
28-Port Gigabit Managed SFP Switch NA NA
System Settings
The System Summary page provides a graphic view of the device, and displays
device status, hardware information, firmware version information, general PoE
status, and other items.
No. of
Ports that
Support
PoE
Displaying the System Summary
To view system information:
STEP 1 Click Status and Statistics > System Summary.
System Information:
• System Operational Mode—A description of the system operation mode
• System Description—A description of the system.
• System Location—Physical location of the device. Click Edit to go the
System Settings page to enter this value.
• System Contact—Name of a contact person. Click Edit to go the System
Settings page to enter this value.
75 Cisco 300 Series Managed Switches Administration Guide
Page 78
Administration
System Settings
5
• Host Name—Name of the device. Click Edit to go the System Settings
page to enter this value. By default, the device hostname is composed of
the word device concatenated with the three least significant bytes of the
device MAC address (the six furthest right hexadecimal digits).
• System Object ID—Used by the system to manage device features
• System Uptime—Time that has elapsed since the last reboot.
• Current Time—Current system time.
• Base MAC Address—Device MAC address.
• Jumbo Frames—Jumbo frame support status. This support can be enabled
or disabled by using the Port Settings page of the Port Management menu.
NOTE Jumbo frames support takes effect only after it is enabled, and after
the device is rebooted.
TCP/UDP Services Status:
• HTTP Service—Displays whether HTTP is enabled/disabled.
• HTTPS Service—Displays whether HTTPS is enabled/disabled.
• SNMP Service—Displays whether SNMP is enabled/disabled.
• Tel net Se rv ic e—Displays whether Telnet is enabled/disabled.
• SSH Service—Displays whether SSH is enabled/disabled.
Software Information:
• Firmware Version (Active Image)—Firmware version number of the active
image.
• Firmware MD5 Checksum (Active Image)—MD5 checksum of the active
image.
• Firmware Version (Non-active)—Firmware version number of the non-
active image.
• Firmware MD5 Checksum (Non-active Image)—MD5 checksum of the
non-active image.
• Boot Version—Boot version number.
• Boot MD5 Checksum—MD5 checksum of the boot version.
• Locale—Locale of the first language. (This is always English).
Cisco 300 Series Managed Switches Administration Guide 76
Page 79
5
Administration
System Settings
• Language Version—Language package version of the first or English
language.
• Language MD5 Checksum—MD5 checksum of the language file.
PoE Power Information: (on devices supporting PoE)
• Maximum Available PoE Power (W)—Maximum available power that can
be delivered by the PoE.
• Total PoE Power Consumption (W)—To ta l PoE power de livered to
connected PoE devices.
• PoE Power Mode—Port Limit or Class Limit.
System Settings
To enter system settings:
STEP 1 Click Administration > System Settings.
STEP 2 View or modify the system settings.
• System Description—Displays a description of the device.
• System Location—Enter the physical location of the device.
• System Contact—Enter the name of a contact person.
• Host Name—Select the host name of this device. This is used in the prompt
of CLI commands:
- Use Default—The default hostname (System Name) of these switches is:
switch123456, where 123456 represents the last three bytes of the
device MAC address in hex format.
- User Defined—Enter the hostname. Use only letters, digits, and hyphens.
Host names cannot begin or end with a hyphen. No other symbols,
punctuation characters, or blank spaces are permitted (as specified in
RFC1033, 1034, 1035).
• System Mode—Select the system mode of this device.
NOTE If you change the system mode after clicking Apply, the system will
require a reboot, and the startup configuration file will be removed after the
boot.
- L2—Select to place the device in Layer 2 system mode.
77 Cisco 300 Series Managed Switches Administration Guide
Page 80
Administration
Console Settings (Autobaud Rate Support)
- L3—Select to place the device in Layer 3 system mode.
• Custom Banner Settings—The following banners can be set:
- Login Banner—Enter text to display on the Login page before login.
Click Preview to view the results.
- Welcome Banner—Enter text to display on the Login page after login.
Click Preview to view the results.
NOTE When you define a login banner from the web-based configuration
utility, it also activates the banner for the CLI interfaces (Console, Telnet, and
SSH).
STEP 3 Click Apply to save the values in the Running Configuration file.
5
Console Settings (Autobaud Rate Support)
The console port speed can be set to one of the following speeds: 4800, 9600,
19200, 38400, 57600, and 115200 or to Auto Detection.
If Auto Detection is selected, the device detects console speed automatically.
When Auto Detection is not enabled, the console port speed is automatically set to
the last speed that was set manually at (115,200 by default).
When Auto Detection is enabled but the console baud-rate has not yet been
discovered, the system uses speed 115,200 for displaying text (for example, the
boot-up information).
After Auto Detection is enabled in the Console Settings page, it can be activated
by connecting the console to the device and pressing the Enter key twice. The
device detects the baud rate automatically.
To enable Auto Detection or to manually set the baud rate of the console:
STEP 1 Click Administration > Console Settings.
STEP 2 Select one of the following:
• Auto Detection—The console baud rate is detected automatically.
• Static—Select one of the available speeds.
Cisco 300 Series Managed Switches Administration Guide 78
Page 81
5
Management Interface
See IPv4 Management and Interfaces.
User Accounts
See Defining Users.
Defining Idle Session Timeout
The
Idle Session Timeout
sessions can remain idle before they timeout and you must log in again to
reestablish one of the following sessions:
configures the time intervals that the management
Administration
Management Interface
STEP 1 Click Administration > Idle Session Timeout.
STEP 2 Select the timeout for the each session from the corresponding list. The default
STEP 3 Click Apply to set the configuration settings on the device.
Time Settings
• HTTP Session Timeout
• HTTPS Session Timeout
• Console Session Timeout
• Telnet Session Timeout
• SSH Session Timeout
To set the idle session timeout for various types of sessions:
timeout value is 10 minutes.
See Administration: Time Settings.
79 Cisco 300 Series Managed Switches Administration Guide
Page 82
Administration
System Log
System Log
See Administration: System Log.
File Management
See Administration: File Management.
Rebooting the Device
Some configuration changes, such as enabling jumbo frame support, require the
system to be rebooted before they take effect. However, rebooting the device
deletes the Running Configuration, so it is critical that the Running Configuration is
saved to the Startup Configuration before the device is rebooted. Clicking Apply
does not save the configuration to the Startup Configuration. For more information
on files and file types, see the System Files section.
5
You can back up the device configuration by using
Management > Copy/Save Configuration
window. You can also upload the configuration from a remote device. See the
Download/Backup Configuration/Log section.
You might want to set the time of the reboot for some time in the future. This could
happen, for example, in one of the following cases:
• You are performing actions on a remote device, and these actions might
create loss of connectivity to the remote device. Pre-scheduling a reboot
restores the working configuration and enables restoring the connectivity to
the remote device. If these actions are successful, the delayed reboot can
be cancelled.
• Reloading the device cause loss of connectivity in the network, thus by
using delayed reboot, you can schedule the reboot to a time that is more
convenient for the users (e.g. late night).
To reboot the device:
STEP 1 Click Administration > Reboot.
STEP 2 Click the Reboot button to reboot the device.
or clicking Save at the top of the
Administration > File
Cisco 300 Series Managed Switches Administration Guide 80
Page 83
5
Administration
Rebooting the Device
• Reboot—Reboots the device. Since any unsaved information in the Running
Configuration is discarded when the device is rebooted, you must click Save
in the upper-right corner of any window to preserve current configuration
across the boot process. If the Save option is not displayed, the Running
Configuration matches the Startup Configuration and no action is necessary.
• Cancel Reboot—Cancels a reboot if one has been schedule for the future.
The following options are available:
- Immediate—Reboot immediately.
- Date—Enter the date (month/day) and time (hour and minutes) of the
schedule reboot. This schedules a reload of the software to take place
at the specified time (using a 24-hour clock). If you specify the month
and day, the reload is scheduled to take place at the specified time and
date. If you do not specify the month and day, the reload takes place at
the specified time on the current day (if the specified time is later than
the current time) or on the next day (if the specified time is earlier than
the current time). Specifying 00:00 schedules the reload for midnight.
The reload must take place within 24 days.
NOTE This option can only be used if the system time has either been set
manually or by SNTP.
- In—Reboot within the specified number of hours and minutes. The
maximum amount of time that can pass is 24 days.
• Restore to Factory Defaults—Reboots the device by using the factory
default configuration. This process erases the Startup Configuration file and
the backup configuration file.
The mirror configuration file is not deleted when restoring to factory
defaults.
• Clear Startup Configuration File—Check to clear the startup configuration
on the device for the next time it boots up.
NOTE Clearing the Startup Configuration File and Rebooting is not the same
as Rebooting to Factory Defaults. Rebooting to Factory Defaults is more
intrusive.
81 Cisco 300 Series Managed Switches Administration Guide
Page 84
Administration
Routing Resources
Routing Resources
Use the Routing Resources page to display TCAM allocation and modify total
TCAM size in Layer 3 mode. TCAM entries are divided into the following groups:
• IP Entries—TCAM entries reserved for IP static routes, IP addresses on the
• Non-IP Entries—TCAM entries reserved for other applications, such as
5
device, and IP hosts. Each type generates the following number of TCAM
entries:
- IPv4 static routes—One entry per route
- IP Addresses—Two entries per IP address
- IP Hosts—One entry per host
ACL rules, CoS policers, and VLAN rate limits.
To view and modify routing resources when the device is in Layer 3 mode:
STEP 1 Click Administration > Routing Resources.
The following fields are displayed:
• Neighbors (1 TCAM entry per neighbor)—Count is the number of
neighbors recorded on the device and TCAM Entries is the total number of
TCAM entries being used for neighbors.
• Interfaces (2 TCAM entry per interface)—Count is the number of IP
addresses on interfaces on the device and TCAM Entries is the total number
of TCAM entries being used for the IP addresses.
• Routes (1 TCAM entry per route)—Count is the number of routes recorded
on the device and TCAM Entries is the total number of TCAM entries being
used for the routes.
• To ta l —Displays the number of TCAM entries that are currently being used.
• Maximum Entries—Select one of the following options:
- Use Default—The number of TCAM entries available for IP entries is
25% of the TCAM size.
- User Defined—Enter a value.
TCAM Resources Table
The following fields are displayed for each unit:
Cisco 300 Series Managed Switches Administration Guide 82
Page 85
5
Administration
Health
• Maximum TCAM Entries for IPv4 and Non-IP Rules—Number of TCAM
entries available for routing and Multicast routing.
• IPv4 Routing
- In Use—Number of TCAM entries utilized for IPv4 routing.
- Maximum—Maximum number of TCAM entries available for IPv4
Routing.
• Non-IP Rules
- In Use—Number of TCAM entries utilized for non-IP rules.
- Maximum—Maximum number of TCAM entries available for non-IP
rules.
You must save your current configuration before changing the TCAM Allocation
Settings.
Health
NOTE A summary of the TCAM entries actually in use and available is displayed at the
bottom of this page. For an explanation of the fields, see TCAM Utilization.
STEP 2 Save the new settings by clicking Apply. This checks the feasibility of the TCAM
allocation. If it is incorrect, an error message is displayed. If it is correct, the
allocation is saved to the Running Configuration file and a reboot is performed.
The Health page monitors the fan status on all devices with fans. Depending on the
model, there are one or more fans on a device. Some models have no fans at all.
Some devices have a temperature sensor to protect its hardware from
overheating. In this case, the following actions are performed by the device if it
overheats and during the cool down period after overheating:
Event Action
At least one temperature
sensor exceeds the
Warning threshold
The following are generated:
• SYSLOG message
• SNMP trap
83 Cisco 300 Series Managed Switches Administration Guide
Page 86
Administration
Health
5
Event Action
At least one temperature
sensor exceeds the Critical
threshold
Cool down period after the
Critical threshold was
exceeded (all sensors are
lower than the Warning
threshold - 2 °C).
The following are generated:
• SYSLOG message
• SNMP trap
The following actions are performed:
• System LED is set to solid amber (if hardware
supports this).
• Disable Ports — When the Critical
temperature has been exceeded for two
minutes, all ports will be shut down.
• (On devices that support PoE) Disable the
PoE circuitry so that less power is consumed
and less heat is emitted.
After all the sensors cool down to Warning
Threshold minus 2 degree C, the PHY will be reenabled, and all ports brought back up.
If FAN status is OK, the ports are enabled.
(On devices that support PoE) the PoE circuitry is
enabled.
To view the device health parameters, click Status and Statistics > Health.
The Health page displays the following fields:
• Fan Status—Fan status. The following values are possible:
- OK—Fan is operating normally.
- Fail—Fan is not operating correctly.
- N/A—Fan ID is not applicable for the specific model.
• Fan Direction—(On relevant devices) The direction that the fans are
working in (for example: Front to Back).
• Te mp e rat ur e—The op ti on s are:
- OK—The temperature is below the warning threshold.
Cisco 300 Series Managed Switches Administration Guide 84
Page 87
5
- Warning—The temperature is between the warning threshold to the
- Critical—Temperature is above the critical threshold
Diagnostics
See Administration: Diagnostics.
Discovery - Bonjour
Administration
Diagnostics
critical threshold.
See Bonjour.
Discovery - LLDP
See Configuring LLDP.
Discovery - CDP
See Configuring CDP.
Ping
The Ping utility tests if a remote host can be reached and measures the round-trip
time for packets sent from the device to a destination device.
Ping operates by sending Internet Control Message Protocol (ICMP) echo request
packets to the target host and waiting for an ICMP response, sometimes called a
pong. It measures the round-trip time and records any packet loss.
85 Cisco 300 Series Managed Switches Administration Guide
Page 88
Administration
Ping
5
To ping a host:
STEP 1 Click Administration > Ping.
STEP 2 Configure ping by entering the fields:
• Host Definition—Select whether to specify the source interface by its IP
address or name. This field influences the interfaces that are displayed in the
Source IP field, as described below.
• IP Version—If the source interface is identified by its IP address, select
either IPv4 or IPv6 to indicate that it will be entered in the selected format.
• Source IP—Select the source interface whose IPv4 address will be used as
the source IPv4 address for communication with the destination. If the Host
Definition field was By Name, all IPv4 and IPv6 addresses will be displayed
in this drop-down field. If the Host Definition field was By IP Address, only the
existing IP addresses of the type specified in the IP Version field will be
displayed.
NOTE If the Auto option is selected, the system computes the source
address based on the destination address.
• Destination IPv6 Address Type—Select Link Local or Global as the type of
IPv6 address to enter as the destination IP address.
- Link Local—The IPv6 address uniquely identifies hosts on a single
network link. A link local address has a prefix of FE80, is not routable, and
can be used for communication only on the local network. Only one link
local address is supported. If a link local address exists on the interface,
this entry replaces the address in the configuration.
- Global—The IPv6 address is a global Unicast IPV6 type that is visible and
reachable from other networks.
• Link Local Interface—If the IPv6 address type is Link Local, select from
where it is received.
• Destination IP Address/Name—Address or host name of the device to be
pinged. Whether this is an IP address or host name depends on the Host
Definition.
• Ping Interval—Length of time the system waits between ping packets. Ping
is repeated the number of times configured in the Number of Pings field,
whether the ping succeeds or not. Select to use the default interval or
specify your own value.
Cisco 300 Series Managed Switches Administration Guide 86
Page 89
5
STEP 3 Click Activate Ping to ping the host. The ping status appears and a message is
STEP 4 View the results of ping in the Ping Counters and Status section of the page.
Traceroute
Administration
Traceroute
• Number of Pings—The number of times the ping operation is performed.
Select to use the default or specify your own value.
• Status—Displays whether the ping succeeded or failed.
added to the list of messages, indicating the result of the ping operation.
Traceroute discovers the IP routes along which packets were forwarded by
sending an IP packet to the target host and back to the device. The Traceroute
page shows each hop between the device and a target host, and the round-trip
time to each such hop.
STEP 1 Click Administration > Traceroute.
STEP 2 Configure Traceroute by entering information into the following fields:
• Host Definition—Select whether hosts are identified by their IP address or
name.
• IP Version—If the host is identified by its IP address, select either IPv4 or
IPv6 to indicate that it will be entered in the selected format.
• Source IP—Select the source interface whose IPv4 address will be used as
the source IPv4 address for communication messages. If the Host Definition
field was By Name, all IPv4 and IPv6 addresses will be displayed in this
drop-down field. If the Host Definition field was By IP Address, only the
existing IP addresses of the type specified in the IP Version field will be
displayed.
• Host IP Address/Name—Enter the host address or name.
• TTL—Enter the maximum number of hops that Traceroute permits. This is
used to prevent a case where the sent frame gets into an endless loop. The
Traceroute command terminates when the destination is reached or when
this value is reached. To use the default value (30), select Use Default.
• Timeout—Enter the length of time that the system waits for a frame to return
before declaring it lost, or select Use Default.
STEP 3 Click Activate Traceroute. The operation is performed.
87 Cisco 300 Series Managed Switches Administration Guide
Page 90
Administration
Traceroute
5
A page appears showing the Round Trip Time (RTT) and status for each trip in the
fields:
• Index—Displays the number of the hop.
• Host—Displays a stop along the route to the destination.
• Round Trip Time (1-3)—Displays the round trip time in (ms) for the first
through third frame and the status of the first through third operation.
Cisco 300 Series Managed Switches Administration Guide 88
Page 91
5
Administration
Traceroute
89 Cisco 300 Series Managed Switches Administration Guide
Page 92
Administration
Traceroute
5
Cisco 300 Series Managed Switches Administration Guide 90
Page 93
5
Administration
Traceroute
91 Cisco 300 Series Managed Switches Administration Guide
Page 94
Administration
Traceroute
5
Cisco 300 Series Managed Switches Administration Guide 92
Page 95
5
Administration
Traceroute
93 Cisco 300 Series Managed Switches Administration Guide
Page 96
Administration: Time Settings
Synchronized system clocks provide a frame of reference between all devices on
the network. Network time synchronization is critical because every aspect of
managing, securing, planning, and debugging a network involves determining
when events occur. Without synchronized clocks, accurately correlating log files
between devices when tracking security breaches or network usage is
impossible.
Synchronized time also reduces confusion in shared file systems, as it is important
for the modification times to be consistent, regardless of the machine on which the
file systems reside.
6
For these reasons, it is important that the time configured on all of the devices on
the network is accurate.
NOTE The device supports Simple Network Time Protocol (SNTP) and when enabled, the
device dynamically synchronizes the device time with time from an SNTP server.
The device operates only as an SNTP client, and cannot provide time services to
other devices.
This section describes the options for configuring the system time, time zone, and
Daylight Savings Time (DST). It covers the following topics:
• System Time Options
• SNTP Modes
• Configuring System Time
Cisco 300 Series Managed Switches Administration Guide 94
Page 97
6
System Time Options
System time can be set manually by the user, dynamically from an SNTP server, or
synchronized from the PC running the GUI. If an SNTP server is chosen, the manual
time settings are overwritten when communications with the server are
established.
As part of the boot process, the device always configures the time, time zone, and
DST. These parameters are obtained from the PC running the GUI, SNTP, values
set manually, or if all else fails, from the factory defaults.
Time
The following methods are available for setting the system time on the device:
• Manual—User must manually set the time.
Administration: Time Settings
System Time Options
• From PC—Time can be received from the PC by using browser information.
The configuration of time from the computer is saved to the Running
Configuration file. You must copy the Running Configuration to the Startup
Configuration to enable the device to use the time from the computer after
reboot. The time after reboot is set during the first WEB login to the device.
When you configure this feature for the first time, if the time was not already
set, the device sets the time from the PC.
This method of setting time works with both HTTP and HTTPS connections.
• SNTP—Time can be received from SNTP time servers. SNTP ensures
accurate network time synchronization of the device up to the millisecond by
using an SNTP server for the clock source. When specifying an SNTP server,
if choosing to identify it by hostname, three suggestions are given in the GUI:
- time-a.timefreq.bldrdoc.gov
- time-b.timefreq.bldrdoc.gov
- time-c.timefreq.bldrdoc.gov
After the time has been set by any of the above sources, it is not set again by the
browser.
NOTE SNTP is the recommended method for time setting.
95 Cisco 300 Series Managed Switches Administration Guide
Page 98
Administration: Time Settings
SNTP Modes
Time Zone and Daylight Savings Time (DST)
The Time Zone and DST can be set on the device in the following ways:
• Dynamic configuration of the device through a DHCP server, where:
• Manual configuration of the time zone and DST becomes the Operational
6
- Dynamic DST, when enabled and available, always takes precedence
over the manual configuration of DST.
- If the server supplying the source parameters fails, or dynamic
configuration is disabled by the user, the manual settings are used.
- Dynamic configuration of the time zone and DST continues after the IP
address lease time has expired.
time zone and DST, only if the dynamic configuration is disabled or fails.
SNTP Modes
NOTE The DHCP server must supply DHCP option 100 in order for dynamic
time zone configuration to take place.
The device can receive system time from an SNTP server in one of the following
ways:
• Client Broadcast Reception (passive mode)—SNTP servers broadcast
the time, and the device listens to these broadcasts. When the device is in
this mode, there is no need to define a Unicast SNTP server.
• Client Broadcast Transmission (active mode)—T he device , a s a n S NTP
client, periodically requests SNTP time updates. This mode works in either
of the following ways:
- SNTP Anycast Client Mode—The device broadcasts time request
packets to all SNTP servers in the subnet, and waits for a response.
- Unicast SNTP Server Mode—The device sends Unicast queries to a list
of manually-configured SNTP servers, and waits for a response.
The device supports having all of the above modes active at the same time and
selects the best system time received from an SNTP server, according to an
algorithm based on the closest stratum (distance from the reference clock).
Cisco 300 Series Managed Switches Administration Guide 96
Page 99
6
Configuring System Time
Selecting Source of System Time
Use the System Time page to select the system time source. If the source is
manual, you can enter the time here.
!
CAUTION If the system time is set manually and the device is rebooted, the manual time
settings must be reentered.
To define system time:
Administration: Time Settings
Configuring System Time
STEP 1 Click Administration > Time Settings > System Time.
The following fields are displayed:
• Actual Time (Static)—System time on the device. This shows the DHCP
time zone or the acronym for the user-defined time zone if these were
defined.
• Last Synchronized Server—Address, stratum and type of the SNTP server
from which system time was last taken.
STEP 2 Enter the following parameters:
Clock Source Settings—Select the source used to set the system clock.
• Main Clock Source (SNTP Servers)—If this is enabled, the system time is
obtained from an SNTP server. To use this feature, you must also configure a
connection to an SNTP server in the SNTP Interface Settings page.
Optionally, enforce authentication of the SNTP sessions by using the SNTP
Authentication page.
• Alternate Clock Source (PC via active HTTP/HTTPS sessions)—Select to
set the date and time from the configuring computer using the HTTP
protocol.
NOTE The Clock Source Setting needs to be set to either of the above in
order for RIP MD5 authentication to work. This also helps features that
associate with time, for example: Time Based ACL, Port, 802.1 port
authentication that are supported on some devices.
97 Cisco 300 Series Managed Switches Administration Guide
Page 100
Administration: Time Settings
Configuring System Time
Manual Settings—Set the date and time manually. The local time is used when
there is no alternate source of time, such as an SNTP server:
• Date—Enter the system date.
• Local Time—Enter the system time.
Time Zone Settings—The local time is used via the DHCP server or Time Zone
offset.
• Get Time Zone from DHCP—Select to enable dynamic configuration of the
6
time zone and the DST from the DHCP server. Whether one or both of these
parameters can be configured depends on the information found in the
DHCP packet. If this option is enabled, DHCP client must be enabled on the
device.
NOTE The DHCP Client supports Option 100 providing dynamic time zone
setting.
• Time Zone from DHCP—Displays the acronym of the time zone configured
from the DHCP server. This acronym appears in the Actual Time field
• Time Zone Offset—Select the difference in hours between Greenwich
Mean Time (GMT) and the local time. For example, the Time Zone Offset for
Paris is GMT +1, while the Time Zone Offset for New York is GMT – 5.
• Time Zone Acronym—Enter a name that will represent this time zone. This
acronym appears in the Actual Time field.
Daylight Savings Settings—Select how DST is defined:
• Daylight Savings—Select to enable Daylight Saving Time.
• Time S et O ffs et—Enter the number of minutes offset from GMT ranging from
1—1440. The default is 60.
• Daylight Savings Type—Click one of the following:
USA
-
-
—DST is set according to the dates used in the USA.
European
Union and other countries that use this standard.
—DST is set according to the dates used by the European
By dates
-
or a European country. Enter the parameters described below.
-
Recurring
Selecting
Cisco 300 Series Managed Switches Administration Guide 98
—DST is set manually, typically for a country other than the USA
—DST occurs on the same date every year.
By Dates
allows customization of the start and stop of DST:
 Loading...