

Page 1

SonicWall NSsp™ 15700
Datasheet
The SonicWall Network Security
services platform™ (NSsp) 15700 is a
next-generation rewall with high port
density and multi-gig speed interfaces,
that can process several million
connections for zero-day and advanced
threats. Designed for large enterprise,
higher education, government agencies
and MSSPs, it eliminates attacks in real
time without slowing performance. It is
designed to be highly reliable and deliver
uninterrupted services to organizations.
Enterprise-Class High-Speed
Firewall
As businesses evolve along with an
increase in managed and unmanaged
devices, networks, cloud workloads,
SaaS applications, users, Internet
speeds, and encrypted connections,
a rewall that can’t support any one of
these becomes a bottleneck in the IT
landscape. A rewall should be a source
of strength and not a point of weakness.
The SonicWall NSsp 15700’s multiple
100G/40G/10G interfaces allow you to
process several million simultaneous
encrypted and unencrypted connections
with unparallel threat prevention
technology. With 70% of all sessions
being encrypted, having a rewall
that can process and examine this
trafc without impacting the end user
experience is critical to productivity and
information security.
The NSsp 15700’s unied policy
interface enables organizations to simply
and intuitively create access and security
policies in a single unied interface.
Simplied management
andreporting
Ongoing management, monitoring
and reporting of network activities
are handled through the SonicWall
Network Security Manager (pending).
This provides an intuitive dashboard
for managing rewall operations as
well as provide historical repor ts –
from a single source. Together, the
simplied deployment and setup along
with the ease of management enable
organizations to lower their total cost
of ownership and realize a high return
oninvestment.
SonicWall NSsp 15700 Benets:
• High por t density
• 100 GbE ports
• Multi-instance rewall
• Integrates with on-prem and
cloud-based sandboxing
• Single pane of glass management
through cloud or rewall
• Redundant power
• SonicOSX 7.0 support
• TLS 1.3 support
• Supports millions of simultaneous
TLS connections
• Low TCO
Page 2

Deployment
Next-Generation Firewall (NGFW)
Wire Mode Functionality
Intrusion Prevention System (IPS)
• Managed through a single pane of glass
• NSsp 15700 integrates with the rest of
the SonicWall ecosystem of solutions
• Gain full visibility into your network
to see what applications, devices,
and users are doing to enforce policies
as well as eliminate threats and
bandwidth bottlenecks
• Integrate with Capture ATP with RTDMI
for cloud-based sandboxing or Capture
Security appliance for on-premise
malware detection
Deep Packet Inspection of SSL/TLS
(DPI-SSL) for hidden threats
• The NSsp 15700 provides inspection
for over millions of simultaneous TLS/
SSL and SSH encrypted connections
regardless of port or protocol
• Inclusion and exclusion rules allow
customization based on specic
organizational compliance and/or
legal requirements
• Support for TL S cipher suites
up to TLS 1.3
Segmentation and Networking
• Operate across several segmented
networks, clouds, or service denitions,
with unique templates, device groups,
and policies across multiple devices
and tenants
• MSSPs can also support multiple
customers with a clean pipe along
with unique policies
Mutli-Instance Firewall
• Multi-instance is the next generation
of multi-tenancy
• Each tenant is isolated with dedicated
compute resources to avoid resource
starvation
• It features physical and logical
ports/tenants
• It supports independent tenant policy
and conguration management
• Leverage version independence and
High Availability (HA) support for tenants
• Bypass Mode for the quick and relatively
non-interruptive introduction of rewall
hardware into a network
• Inspec t Mode to extend Bypass Mode
without functionally altering the low-risk,
zero latency packet path
• Secure Mode to actively interposing the
rewall's multi-core processors into the
packet processing path
• Tap Mode to ingest a mirrored packet
stream via a single switch port on
the rewall, eliminating the need for
physically intermediated insertion
Advanced Threat Protection
• SonicWall Capture Advanced Threat
Protec tion™ (ATP) is used by over
150,000 customers across the world
through a variety of solutions and it helps
to discover and stop over 1,200 new
forms of malware each business day
• For compliance and performancesensitive customers, the NSsp 15700
integrates with Capture Security
appliance (CSa), a local device based
on the memory-based le analysis
technology, Real-Time Deep Memory
Inspection™ (RTDMI)
Capture Cloud Platform
• SonicWall's Capture Cloud Platform
delivers cloud-based threat prevention
and network management plus reporting
and analy tics for organizations of any size
Content Filtering Services
• Compare requested web sites against a
massive database in the cloud containing
millions of rated URLs, IP addresses and
web sites
• Create and apply policies that allow or
deny access to sites based on individual
or group identity, or by time of day, for
over 50 pre-dened categories
• Delivers a congurable, high performance
Deep Packet Inspection engine for
extended protection of key network
services such as Web, e-mail, le transfer,
Windows services and DNS
• Designed to protect against application
vulnerabilities as well as worms, trojans,
and peer-to-peer, spyware and
backdoor exploits
• The extensible signature language
provides proac tive defense against
newly discovered application and
protocol vulnerabilities
• SonicWall IPS ofoads the costly and
time-consuming burden of maintaining
and updating signatures for new attacks
through SonicWall's industry-leading
Distributed Enforcement
Architecture (DEA)
IoT and Application Control
• The NSsp 15700 catalogs thousands
of applications through App Control
and monitors their trafc for anomalous
behavior through the on-board
Application Firewall
• Segment managed from unmanaged
devices with unique management
and access proles
2
Page 3
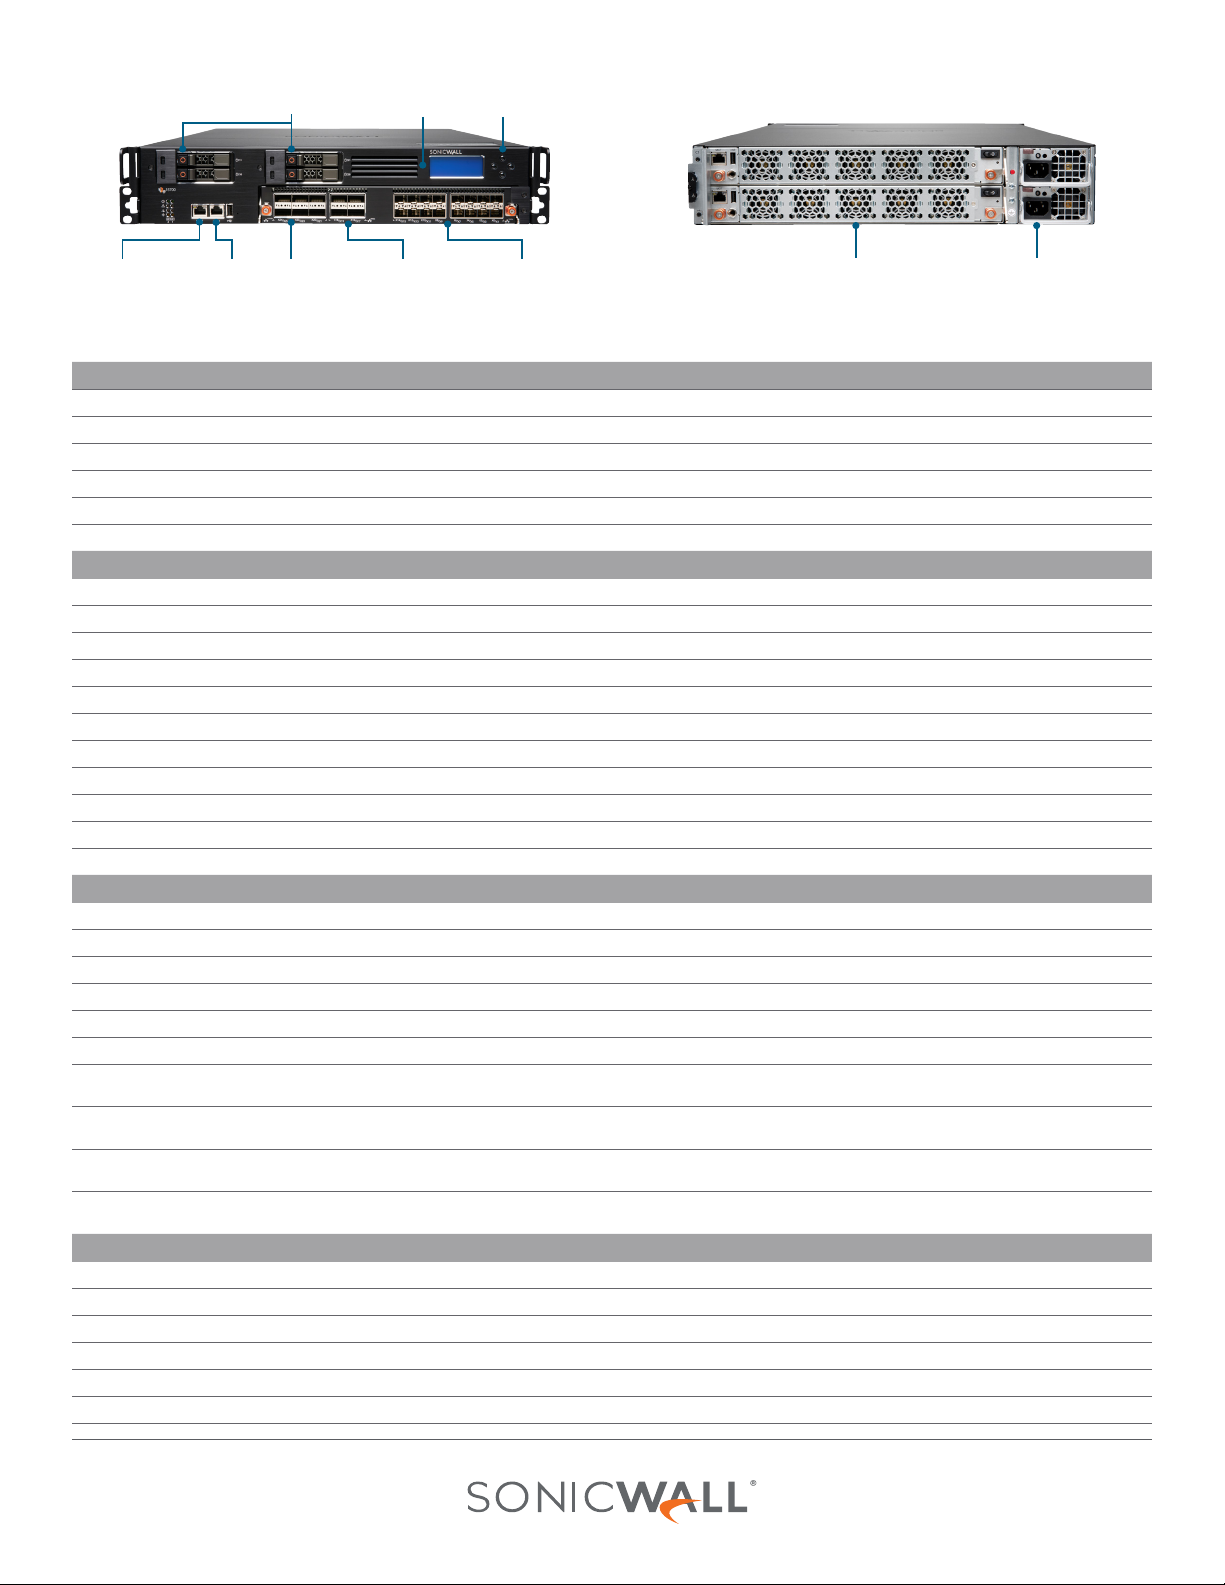
NSsp 15700
Storage modules
LCD controlsLCD display
Management
Console 6x 100-GbE
QSFP28 ports
4x 40-GbE
QSFP+ por ts
16x 10 GbE
SFP+ ports
Dual power supply10x fans
SonicWall NSsp 15700 specications
FIREWALL GENERAL NSsp 15700
Operating System SonicOSX 7
Interfaces 6 x 100-GbE QSFP28, 4 x 40-GbE QSFP+, 16 x 10 GbE SFP+
Built-in storage 2 x 480 GB SSD
Management CLI, SSH, Web UI, REST APIs
SSO Users 100,000
Logging Analyzer, Local Log, Syslog, IPFIX, NetFlow
FIREWALL/VPN PERFORMANCE NSsp 15700
Firewall inspection throughput 105 Gbps
Threat Prevention throughput 82 Gbps
Application inspection throughput 86 Gbps
IPS throughput 76.5 Gbps
IMIX throughput 28.5 Gbps
TLS/SSL inspection and decryption throughput (DPI SSL) 21 Gbps
VPN throughput 32 Gbps
Connections per second 800k
Maximum connections (SPI) 80M
Maximum connections (DPI) 50M
Maximum connections (DPI SSL) 3M
VPN NSsp 15700
Site-to-site VPN tunnels 25,000
IPSec VPN clients (maximum) 2,000 (10,000)
SSL VPN NetExtender clients (maximum) 2 (3,000)
Encryption/authentication DES, 3DES, AES (128, 192, 256-bit)/MD5, SHA-1, Suite B Cryptography
Key exchange Dife Hellman Groups 1, 2, 5, 14v
Route-based VPN RIP, OSPF, BGP
VPN features
Global VPN client platforms supported
NetExtender
Mobile Connect
NETWORKING NSsp 15700
Multi-Instance Firewall Max Tenants per Hardware: 12
IP address assignment Static (DHCP, PPPoE, L2TP and PPTP client), Internal DHCP server, DHCP Relay
NAT modes 1:1, many:1, 1:many, exible NAT (overlapping IP), PAT, transparent mode
VLAN interfaces 512
Wire Mode Yes
Routing protocols BGP, OSPF, RIPv1/v2, static routes, policy-based routing
Microsoft® Windows Vista 32/64-bit, Windows 7 32/64-bit, Windows 8.0 32/64-bit,
Dead Peer Detection, DHCP Over VPN, IPSec NAT Traversal,
Redundant VPN Gateway, Route-based VPN
Windows 8.1 32/64-bit, Windows 10
Microsoft Windows Vista 32/64-bit, Windows 7, Windows 8.0 32/64-bit,
Windows 8.1 32/64-bit, Mac OS X 10.4+, Linux FC3+/Ubuntu 7+/OpenSUSE
Apple® iOS, Mac OS X, Google® Android™, Kindle Fire,
Chrome, Windows 8.1 (Embedded)
3
Page 4
SonicWall NSsp 15700 specications
QoS Bandwidth priority, max bandwidth, guaranteed bandwidth, DSCP marking, 802.1p
Authentication LDAP, XAUTH/RADIUS, SSO, Novell, internal user database, Terminal Services, Citrix
VoIP Full H.323-v1-5, SIP
Standards
Certifications (in progress)
High availability Active/Passive with State Sync
HARDWARE NSsp 15700
Power supply Dual, Redundant, 1,200W
Fans 10
Input power 100-240 VAC, 50-60 Hz
Maximum power consumption (W) 1065
Form factor 2U Rack Mountable
Dimensions 68.6 x 43.8 x 8.8 (cm)
Weight 26 Kg
WEEE weight 30.1 Kg
Shipping weight 37.3 Kg
Shipping dimensions 28 x 63 x 86 (cm)
Major Regulatory
Environment (Operating/Storage) 32°-105° F (0°-40° C)/-40° to 158° F (-40° to 70° C)
Humidity 10-95% non-condensing
TCP/IP, ICMP, HTTP, HTTPS, IPSec, ISAKMP/IKE, SNMP, DHCP, PPPoE, L2TP, PPTP,
RADIUS, IEEE 802.3
ICSA Firewall, ICSA Anti-Virus, FIPS 140-2, Common Criteria NDPP (Firewall and IPS),
UC APL, USGv6, CsFC
FCC Class A, ICES Class A, CE (EMC Class A, LVD, RoHS), C-Tick, VCCI Class A,
MSIP/KCC Class A, UL, cUL, TUV/GS, CB, Mexico UL DGN notication,
WEEE, REACH, ANATEL, BSMI
4
Page 5
SonicOSX feature summary
Firewall
• Stateful packet inspec tion
• Reassembly-Free Deep Packet Inspection
• D DoS attack protection (UDP/ICMP/SYN ood)
• IPv4/IPv6 support
• Biometric authentication for remote access
• D NS prox y
• REST A PIs
• SonicWall Switch integration
Unied Securit y Policy
• Unie d Policy combines Layer 4 to Layer 7 rules:
• Source/Destination IP/Por t/Service
• Application Control
• CFS/Web Filtering
• Single Pass Security Services enforcement
• IPS/GAV/AS/Capture ATP
• Rule management:
• Cloning
• Shadow rule analysis
• In-cell editing
• Group editing
• Managing views
• Used/un-used rules
• Active /in-ac tive rules
• Sections
TLS/SSL/SSH decryption and inspection
• TLS 1. 3
• Deep packet inspe ction for TLS/SSL/ SSH
• Inclusion/exclusion of objects, groups or
hostnames
• SSL cont rol
• Granular DPI-SSL controls per zone or rule
• Decryption Policies for SSL /TLS and SSH
Capture advanced threat protection
2
• Real-Time Deep Memory Inspection
• Cloud-based multi-engine analysis
• Virtualized sandboxing
• Hypervisor level analysis
• Full system emulation
• Broad le type examination
• Automated and manual submission
• Real-time threat intelligence updates
• Block until verdict
• Capture Client integration
Intrusion prevention
2
• Signature-based scanning
• Automatic signature updates
• Bi-directional inspec tion
• Granular IPS rule capability
• GeoIP enforcement
• B otnet ltering wit h dynamic list
• Regular expression matching
Anti-malware
2
• Stream-based malware scanning
• Gateway antivirus
• Gateway anti-spyware
• Bi-directional inspec tion
• N o le size limitat ion
• Cloud malware database
Application identication
2
• Application control
• Application bandwidth management
• Custom application signature creation
• Data leakage prevention
• Application repor ting over Net Flow/ IPFIX
• Comprehensive application signature database
Trafc visualization and analytics
• User act ivity
• Application/bandwidth/threat usage
• Cloud-based analytics
HTTP/HTTPS Web content ltering
2
• URL ltering
• Proxy avoidance
• Keyword blocking
• Policy-based ltering (exclusion/inclusion)
• HTTP header insertion
• Bandwidth manage CFS rating categories
• Content Filtering Client
VPN
• Auto-provision VPN
• I PSec VPN for site-to-site connec tiv ity
• SSL VPN and IPSec client remote access
• Redundant VPN gateway
• M obile Connec t for iOS, Mac OS X, Windows,
Chrome, Android and Kindle Fire
• Route-based VPN (OSPF, RIP, BGP)
Networking
• Multi-instance architecture
• Port Shield
• Jumbo frames
• Path MT U discovery
• Enhanced logging
• VL AN trunking
• Por t mirroring
• L ayer-2 QoS
• Port security
• D ynamic routing (RIP/OSPF/BGP)
• Policy-based routing ( ToS/metric and ECMP)
• N AT
• DHCP server
• Bandwidth management
• Link aggregation1 (static and dynamic)
• Por t redundancy
1
• A/ P high availability with state sync
• A/A clustering
1
• Inbound/outbound load balancing
• High availabilit y - Active/Standby with state
sync
• Wire /virtual wire mode, tap mode, NAT mode
• Asymmetric routing
VoIP
• Granular QoS control
• Bandwidth management
• D PI for VoIP traf c
• H .323 gatekeeper and SIP proxy support
Management and monitoring
• Web GUI
• Command line interface (CLI)
• Zero-Touch registration & provisioning
• SonicExpress mobile app support
• S NMPv2 /v3
• Centralized management and reporting with
SonicWall Global Management System (GMS )
• Logging
• N etow/IPFix expor ting
• Cloud-based conguration backup
• BlueCoat security analytics platform
• Application and bandwidth visualization
• IPv4 and IPv6 management
2
1
Not supported on NSv Series rewalls
2
Requires added subscription.
5
Page 6
Product SKU
SONICWALL NSSP 15700 02-SSC-2722
ESSENTIAL GATEWAY SECURITY SUITE BUNDLE FOR NSSP 15700 1YR 02-SSC-4739
ESSENTIAL GATEWAY SECURITY SUITE BUNDLE FOR NSSP 15700 3YR 02-SSC-4740
ESSENTIAL GATEWAY SECURITY SUITE BUNDLE FOR NSSP 15700 5YR 02-SSC-4741
24X7 SUPPORT FOR NSSP 15700 1YR 02-SSC-4733
24X7 SUPPORT FOR NSSP 15700 3YR 02-SSC-4734
24X7 SUPPORT FOR NSSP 15700 5YR 02-SSC-4735
Bundles SKU
SONICWALL NSSP 15700 TOTALSECURE ESSENTIAL EDITION 1YR 02-SSC-4764
SONICWALL NSSP 15700 TOTALSECURE ESSENTIAL EDITION 3YR 02-SSC-4766
SONICWALL NSSP 15700 TOTALSECURE ESSENTIAL EDITION 5YR 02-SSC-4765
Accessories SKU
10GB-SR SFP+ SHORT REACH FIBER MODULE MULTI-MODE NO CABLE 01-SSC-9785
10GB-LR SFP+ LONG REACH FIBER MODULE SINGLE-MODE NO CABLE 01-SSC-9786
10GB SFP+ COPPER WITH 1M TWINAX CABLE 01-SSC-9787
10GB SFP+ COPPER WITH 3M TWINAX CABLE 01-SSC-9788
1GB-SX SFP SHORT HAUL FIBER MODULE MULTI-MODE NO CABLE 01-SSC-9789
1GB-LX SFP LONG HAUL FIBER MODULE SINGLE-MODE NO CABLE 01-SSC-9790
1GB-RJ45 SFP COPPER MODULE NO CABLE 01-SSC-9791
SONICWALL SFP+ 10GBASE-T TRANSCEIVER COPPER RJ45 MODULE 02-SSC-1874
About SonicWall
SonicWall delivers Boundless Cybersecurity for the hyper-distributed era and a work reality where everyone is remote, mobile
and unsecure. By knowing the unknown, providing real-time visibility and enabling breakthrough economics, SonicWall closes the
cybersecurity business gap for enterprises, governments and SMBs worldwide. For more information, visit www.sonicwall.com
SonicWall, Inc.
1033 McCarthy Boulevard | Milpitas, CA 95035
Refer to our website for additional information.
www.sonicwall.com
© 2021 SonicWall Inc. ALL RIGHTS RESERVED. SonicWall is a
trademark or registered trademark of SonicWall Inc. and/or its afliates
in the U.S.A. and/or other countries. All other trademarks and registered
trademarks are property of their respective owners.
Datasheet-NSsp15700-US-VG-3853
 Loading...