

Page 1
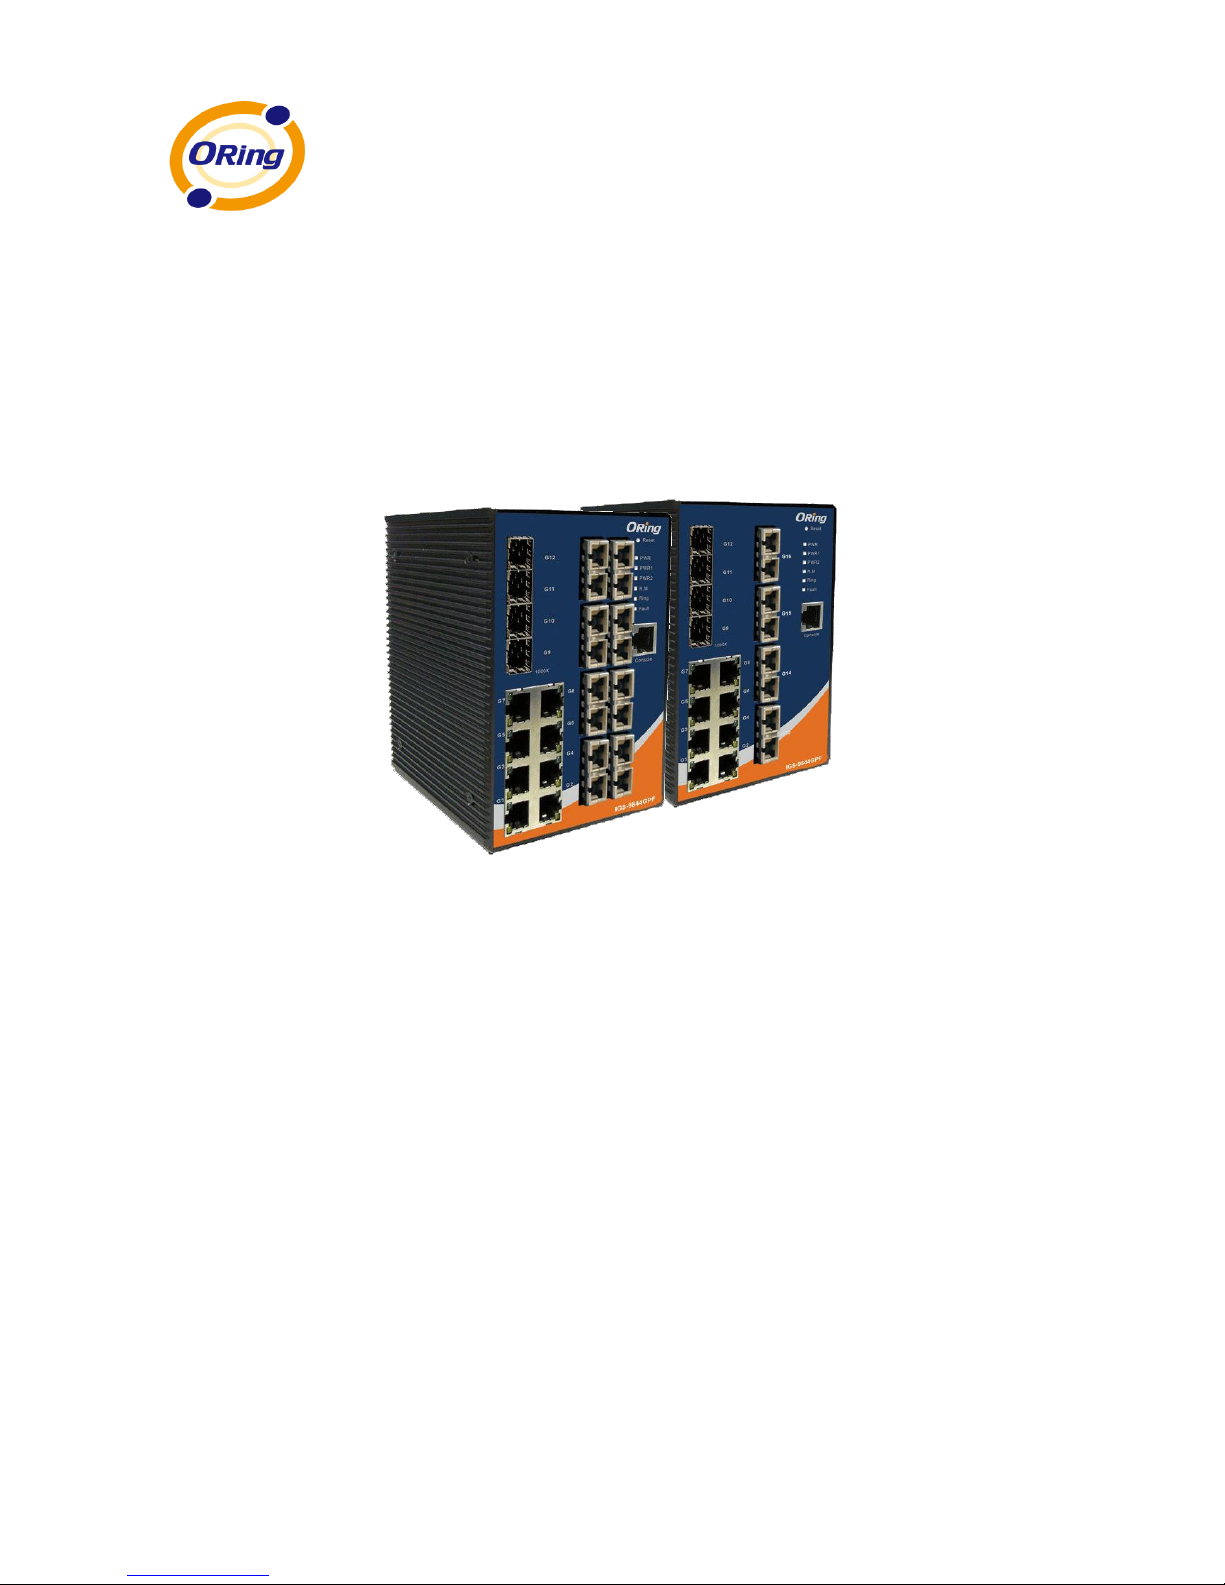
IIGGSS--99884444//99884488GGPPFF
IInndduussttrriiaall MMaannaaggeedd EEtthheerrnneett SSwwiittcchh
UUsseerr M
Maannuuaall
VVeerrssiioonn 33..00
FFeebb,, 22001133
wwwwww..oorriinngg--nneettwwoorrkkiinngg..ccoomm
Page 2
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
1
COPYRIGHT NOTICE
Copyright © 2010 ORing Industrial Networking Corp.
All rights reserved.
No part of this publication may be reproduced in any form without the prior written consent of
ORing Industrial Networking Corp.
TRADEMARKS
is a registered trademark of ORing Industrial Networking Corp.
All other trademarks belong to their respective owners.
REGULATORY COMPLIANCE STATEMENT
Product(s) associated with this publication complies/comply with all applicable regulations.
Please refer to the Technical Specifications section for more details.
WARRANTY
ORing warrants that all ORing products are free from defects in material and workmanship for
a specified warranty period from the invoice date (5 years for most products). ORing will repair
or replace products found by ORing to be defective within this warranty period, with shipment
expenses apportioned by ORing and the distributor. This warranty does not cover product
modifications or repairs done by persons other than ORing-approved personnel, and this
warranty does not apply to ORing products that are misused, abused, improperly installed, or
damaged by accidents.
Please refer to the Technical Specifications section for the actual warranty period(s) of the
product(s) associated with this publication.
DISCLAIMER
Information in this publication is intended to be accurate. ORing shall not be responsible for its
use or infringements on third-parties as a result of its use. There may occasionally be
unintentional errors on this publication. ORing reserves the right to revise the contents of this
publication without notice.
CONTACT INFORMATION
ORing Industrial Networking Corp.
3F., NO.542-2, Jhongjheng Rd., Sindian District, New Taipei City 231, Taiwan, R.O.C.
Tel: + 886 2 2218 1066 // Fax: + 886 2 2218 1014
Website: www.oring-networking.com
Technical Support
E-mail: [email protected]
Sales Contact
E-mail: [email protected] (Headquarters)
[email protected] (China)
Page 3
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
2
Table of Content
Getting Started......................................................................................... 6
1.1 About IGS-9844/9848GPF .................................................................................... 6
1.2 Software Features ................................................................................................ 6
1.3 Hardware Specifications ....................................................................................... 7
Hardware Overview................................................................ .................. 8
2.1 Front Panel........................................................................................................... 8
2.1.1 Ports and Connectors ....................................................................................... 8
2.1.2 LED .................................................................................................................. 9
2.2 Top Panel ........................................................................................................... 10
2.3 Rear Panel ......................................................................................................... 10
Hardware Installation ............................................................................. 11
3.1 DIN-rail Installation ..............................................................................................11
3.2 Wall Mounting ..................................................................................................... 12
3.3 Wiring ................................................................................................................. 14
3.3.1 Grounding ...................................................................................................... 14
3.3.2 Fault Relay ..................................................................................................... 14
3.3.3 Redundant Power Inputs ................................................................................ 14
3.4 Connection ......................................................................................................... 15
3.4.1 Cables ............................................................................................................ 15
3.4.2 SFP ................................................................................................................ 17
3.4.3 O-Ring/O-Chain.............................................................................................. 18
Redundancy........................................................................................... 21
4.1 O-Ring................................................................................................................ 21
4.1.1 Introduction .................................................................................................... 21
4.1.2 Configurations ................................................................................................ 21
4.2 O-Chain.............................................................................................................. 23
4.2.1 Introduction .................................................................................................... 23
4.2.2 Configurations ................................................................................................ 23
4.3 MRP ................................................................................................................... 24
4.3.1 Introduction .................................................................................................... 24
4.3.2 Configurations ................................................................................................ 24
4.4 STP/RSTP/MSTP ............................................................................................... 25
4.4.1 STP/RSTP...................................................................................................... 25
Page 4
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
3
4.4.2 MSTP ................................................................................................ ............. 28
4.4.3 CIST............................................................................................................... 31
4.5 Fast Recovery .................................................................................................... 33
Management ................................ .......................................................... 34
5.1 Basic Settings..................................................................................................... 35
5.1.1 System Information......................................................................................... 35
5.1.2 Admin & Password ......................................................................................... 36
5.1.3 Authentication................................................................................................. 37
5.1.4 IP Settings ................................ ...................................................................... 38
5.1.5 IPv6 Settings ................................ .................................................................. 38
5.1.6 HTTPS ........................................................................................................... 40
5.1.7 SSH ............................................................................................................... 40
5.1.8 LLDP ................................................................................................ .............. 41
5.1.9 Modbus TCP .................................................................................................. 44
5.1.10 Backup/Restore Configurations....................................................................... 45
5.1.11 Firmware Update ............................................................................................ 45
5.2 DHCP Server...................................................................................................... 45
5.2.1 Basic Settings................................................................................................. 45
5.2.2 Dynamic Client List ......................................................................................... 46
5.2.3 Client List ................................ ................................ ....................................... 46
5.2.4 DHCP Relay ................................................................................................... 46
5.3 Port Setting ........................................................................................................ 49
5.3.1 Port Control ................................ .................................................................... 49
5.3.2 Port Trunk................................ ................................ ....................................... 50
5.3.3 LACP.............................................................................................................. 50
5.3.4 Loop Gourd .................................................................................................... 55
5.4 VLAN.................................................................................................................. 56
5.4.1 VLAN Membership ......................................................................................... 56
5.4.2 Port Configurations ......................................................................................... 57
5.4.3 Private VLAN .................................................................................................. 65
5.5 SNMP................................................................................................................. 67
5.5.1 SNMP System Configurations ......................................................................... 67
5.5.2 SNMP Community Configurations ................................................................... 69
5.5.3 SNMP User Configurations ................................................................ ............. 70
5.5.4 SNMP Group Configurations........................................................................... 71
5.5.5 SNMP View Configurations ............................................................................. 72
5.5.6 SNMP Access Configurations ......................................................................... 73
Page 5
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
4
5.6 Traffic Prioritization ................................ ............................................................. 74
5.6.1 Storm Control ................................................................................................. 74
5.6.2 Port Classification ........................................................................................... 75
5.6.3 Port Tag Remaking ......................................................................................... 77
5.6.4 Port DSCP...................................................................................................... 78
5.6.5 Policing .......................................................................................................... 79
5.6.6 Scheduling and Shaping ................................................................................. 80
5.6.7 Port Scheduler................................................................................................ 83
5.6.8 Port Shaping................................................................................................... 84
5.6.9 DSCP-based QoS ................................................................ .......................... 84
5.6.10 DSCP Translation ................................................................ ........................... 85
5.6.11 DSCP Classification........................................................................................ 86
5.6.12 QoS Control List ............................................................................................. 87
5.6.13 QoS Counters................................................................................................. 89
5.6.14 QCL Status ..................................................................................................... 89
5.7 Multicast ............................................................................................................. 91
5.7.1 IGMP Snooping .............................................................................................. 91
5.7.2 VLAN Configurations of IGMP Snooping ................................ ......................... 92
5.7.3 IGMP Snooping Status.................................................................................... 93
5.7.4 Groups Information of IGMP Snooping............................................................ 93
5.8 Security .............................................................................................................. 94
5.8.1 Remote Control Security Configurations ......................................................... 94
5.8.2 Device Binding ............................................................................................... 95
5.8.3 ACL .............................................................................................................. 100
5.8.4 Authentication, Authorization, and Accounting ................................................112
5.8.5 RAIDUS.........................................................................................................112
5.8.6 NAS (802.1x) ................................................................................................ .118
5.9 Alerts ................................................................................................................ 128
5.9.1 Fault Alarm ................................ ................................................................... 128
5.9.2 System Warning ................................................................ ........................... 129
5.10 Monitor and Diag .............................................................................................. 132
5.10.1 MAC Table.................................................................................................... 132
5.10.2 Port Statistics................................................................ ................................ 135
5.10.3 Port Mirroring................................................................................................ 137
5.10.4 System Log Information ................................................................................ 138
5.10.5 Cable Diagnostics......................................................................................... 139
5.10.6 SFP Monitor ................................................................................................ . 140
Page 6
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
5
5.10.7 Ping.............................................................................................................. 141
5.11 Synchronization ................................................................................................ 142
5.12 Troubleshooting ................................................................................................ 144
5.12.1 Factory Defaults ........................................................................................... 144
5.12.2 System Reboot ............................................................................................. 144
5.13 Command Line Interface Management ............................................................. 145
Page 7
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
6
Getting Started
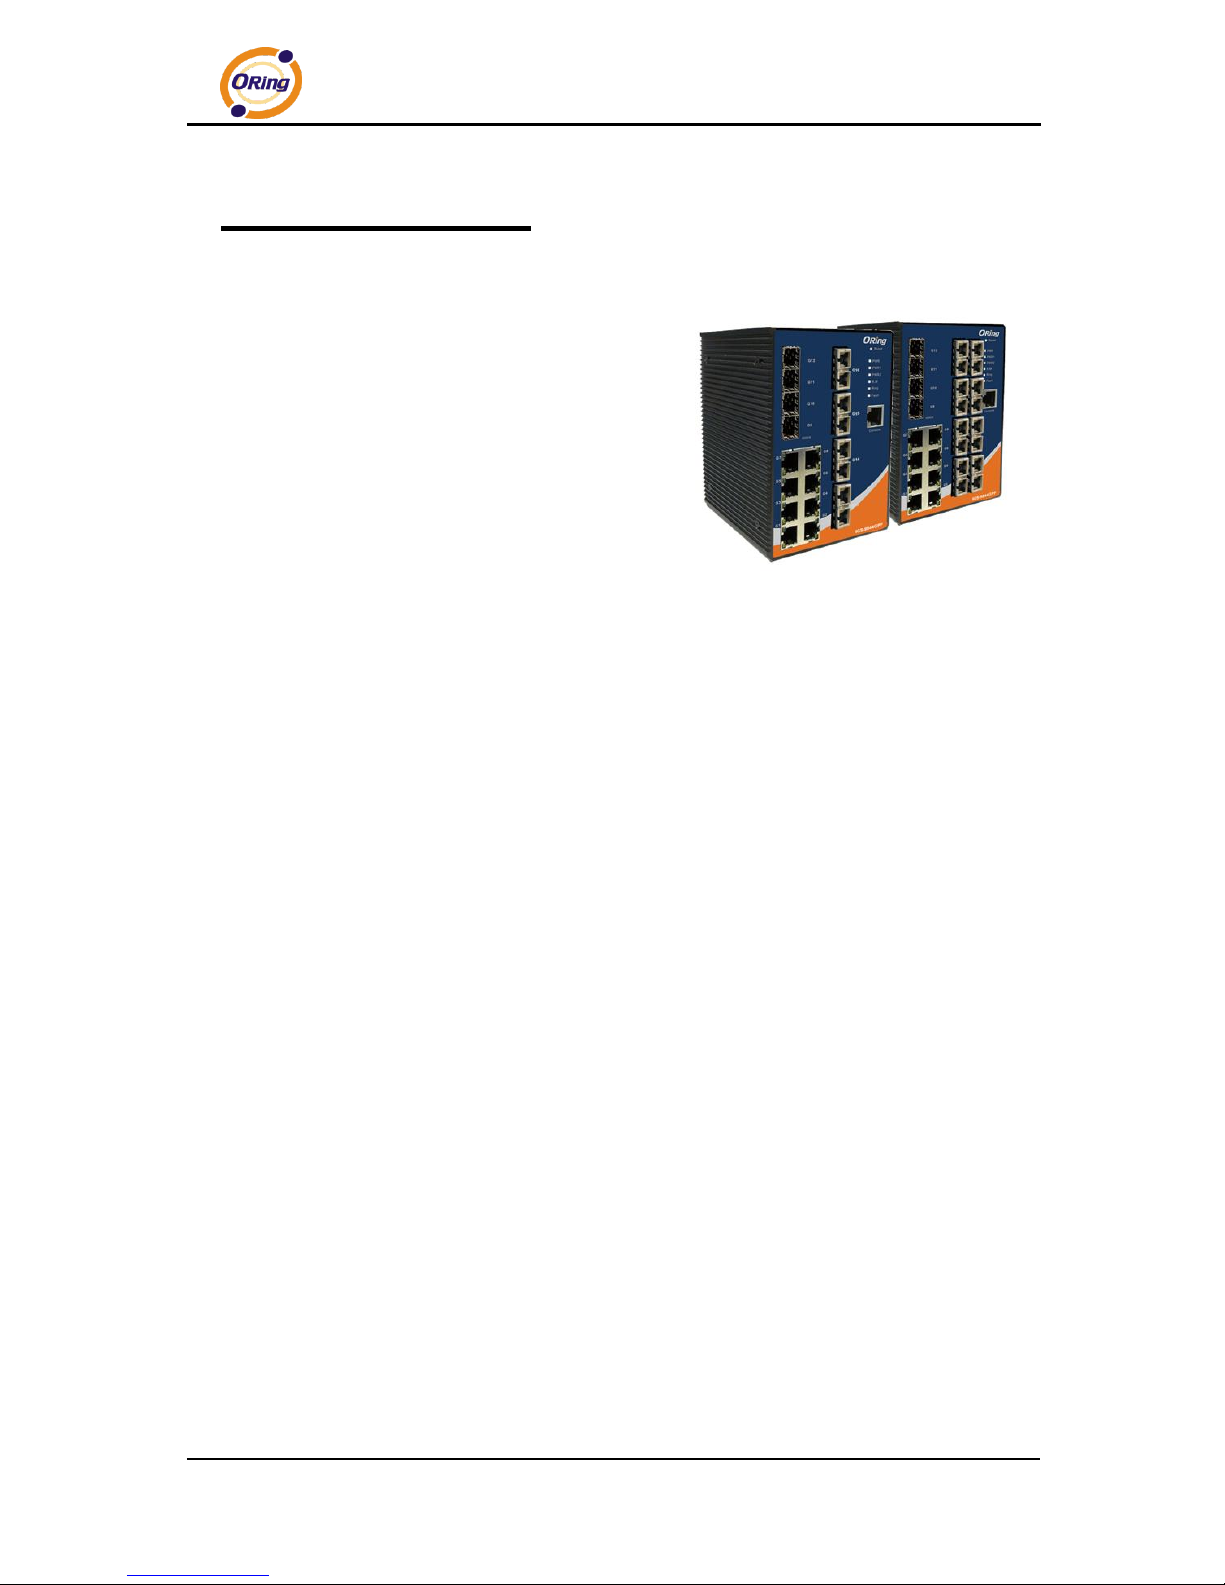
1.1 About IGS-9844/9848GPF
Featuring network redundancy capabilities, the
IGS-9844/9848GPF series are managed Ethernet
switches with eight 10/100/1000Base-T(X) ports, four
100/1000Base-X SFP ports, and four (IGS-9844 GPF
series) or eight (IGS-9848GPF series) 1000Base-X
optical fiber ports with SC connectors. With complete
support for Ethernet redundancy protocols such as
O-Ring (recovery time < 30ms over 250 units of
connection) and MSTP (RSTP/STP compatible), the switch can protect your mission-critical
applications from network interruptions or temporary malfunctions with its fast recovery
technology. Featuring a wide operating temperature from -40oC to 70oC, the
IGS-9844/9848GPF series can be managed centrally and conveniently via Open-Vision, web
browsers, Telnet and console (CLI) configuration, making it one of the most reliable choice for
highly-managed and Fiber Ethernet power substation and rolling stock application
1.2 Software Features
Supports O-Ring (recovery time < 30ms over 250 units of connection) and
MSTP(RSTP/STP compatible) for Ethernet redundancy
Supports Open-Ring to interoperate with other vendors‟ ring technology in open
architecture
Supports O-Chain to allow multiple redundant network rings
Supports standard IEC 62439-2 MRP (Media Redundancy Protocol) function
Supports IEEE 1588v2 clock synchronization
Supports IPV6 new internet protocol version
Supports Modbus TCP protocol
Supports HTTPS/SSH protocols to enhance network security
Supports IEEE 802.3az Energy-Efficient Ethernet technology
Supports SMTP client
Supports IP-based bandwidth management
Supports application-based QoS management
Supports Device Binding security function
Supports DOS/DDOS auto prevention
Supports IGMP v2/v3 (IGMP snooping support) to filter multicast traffic
Page 8
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
7
Supports SNMP v1/v2c/v3 & RMON & 802.1Q VLAN network management
Supports ACL, TACACS+ and 802.1x user authentication for security
Supports 9.6K Bytes Jumbo frame
Supports multiple notifications for incidents
Supports management via Web-based interfaces, Telnet, Console (CLI), and Windows
utility (Open-Vision)
Supports LLDP protocol
1.3 Hardware Specifications
Redundant DC power inputs
Operating Temperature: -40 to 70oC
Storage Temperature: -40 to 85 oC
Operating Humidity: 5% to 95%, non-condensing
Casing: IP-30
8 x 10/100/1000Base-T(X)
4 x 100/1000Base-X SFP ports
4 x 1000Base-X optical fiber ports (IGS-9844 GPF series) or 8 x 1000Base-X
(IGS-9848GPF series) optical fiber ports
1 x console port
Dimensions: 96.4 (W) x 105.5 (D) x 154 (H) mm (3.8 x 4.15 x 6.06 inch)
Page 9
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
8
Hardware Overview
2.1 Front Panel
2.1.1 Ports and Connectors
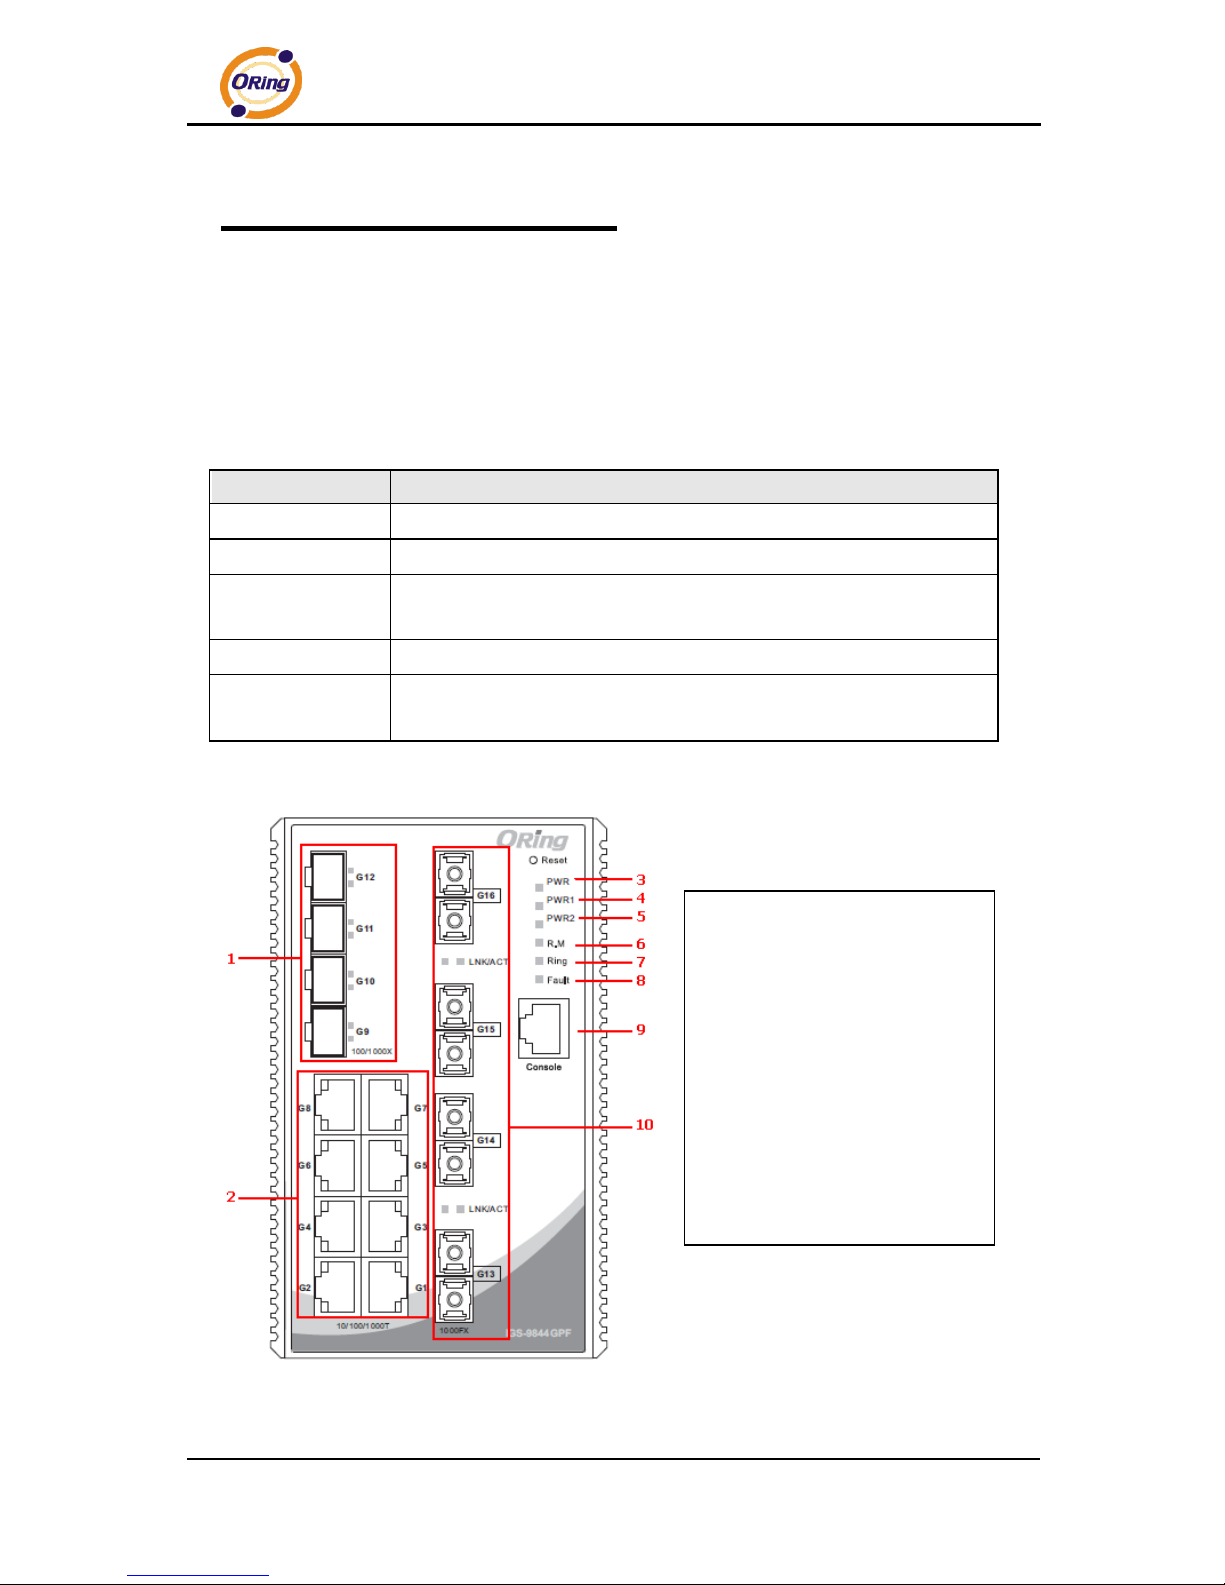
The IGS-9844/9848GPF series provide the following ports on the front panel. The Ethernet
ports on the switches use RJ-45 connectors and the SFP module slots SC style connectors.
Port
Description
Copper port
8 x 10/100/1000Base-T(X)
SFP port
4 x 100/1000Base-X
Fiber port
4 x 1000Base-X (IGS-9844GPF series) or 8 x 1000Base-X
(IGS-9848GPF series), SC connector
Console port
1 console port
Reset button
Press reset button 2 to 3 seconds to reset the switch.
Press reset button 5 seconds to reset the switch to factory defaults.
IGS-9844GPF
1. SFP fiber ports
2. RJ-45 ports
3. Power LED
4. PWR1 LED
5. PWR2 LED
6. Ring Master status LED
7. Ring status LED
8. Faulty relay indicator
9. Console port
10. Fiber ports
Page 10
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
9
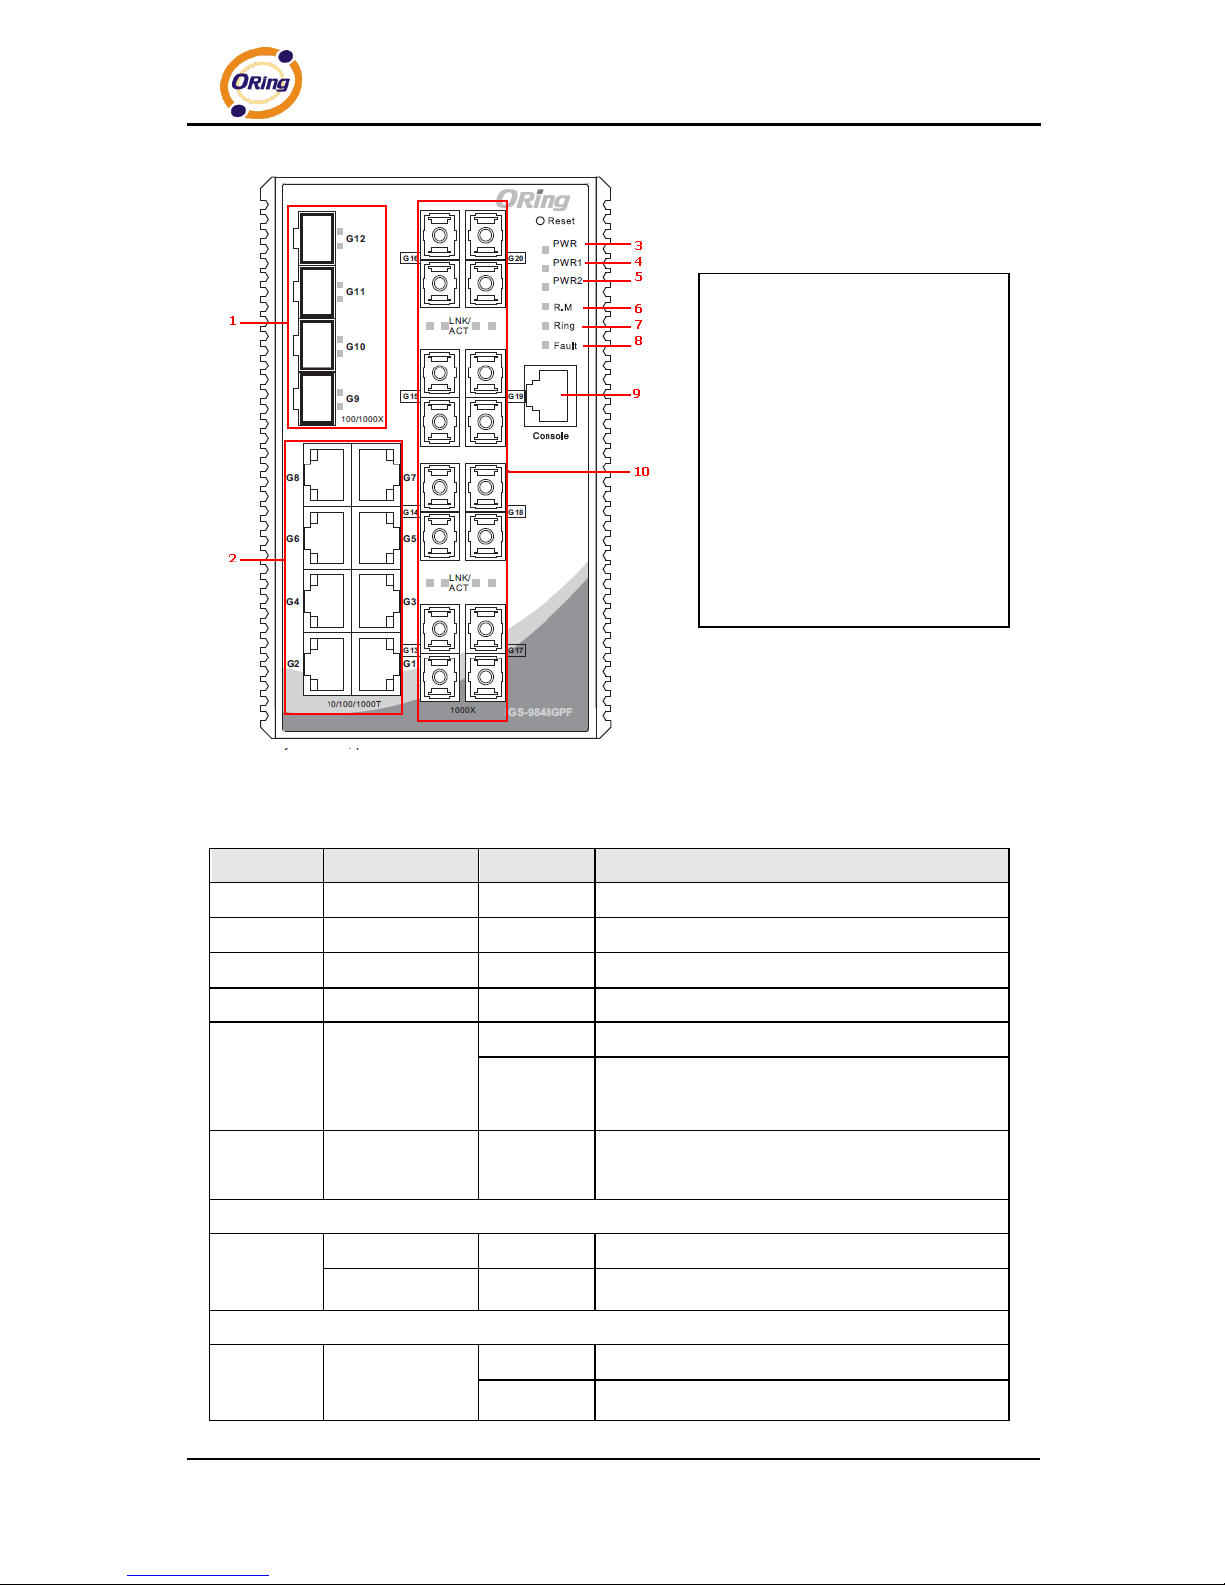
IGS-9848GPF
2.1.2 LED
LED
Color
Status
Description
PWR
Green
On
DC power on
PW1
Green
On
DC power module 1 activated
PW2
Green
On
DC power module 2 activated
R.M
Green
On
Ring Master
Ring
Green
On
Ring enabled
Blinking
Ring structure is broken (i.e. part of the ring is
disconnected)
Fault
Amber
On
Faulty relay (power failure or port
malfunctioning)
10/100/1000Base-T(X) Fast Ethernet ports
Link/Act
Green
On
Ethernet running at 1000Mbps
Amber
On
Ethernet running at 10/100Mbps
SFP & 100Base-FX or 1000Base-X Fiber Port
Link/Act
Green
On
Port link up
On
Transmitting data
1. SFP fiber ports
2. RJ-45 ports
3. Power LED
4. PWR1 LED
5. PWR2 LED
6. Ring Master status LED
7. Ring status LED
8. Faulty relay indicator
9. Console port
10. Fiber ports
Page 11
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
10
2.2 Top Panel
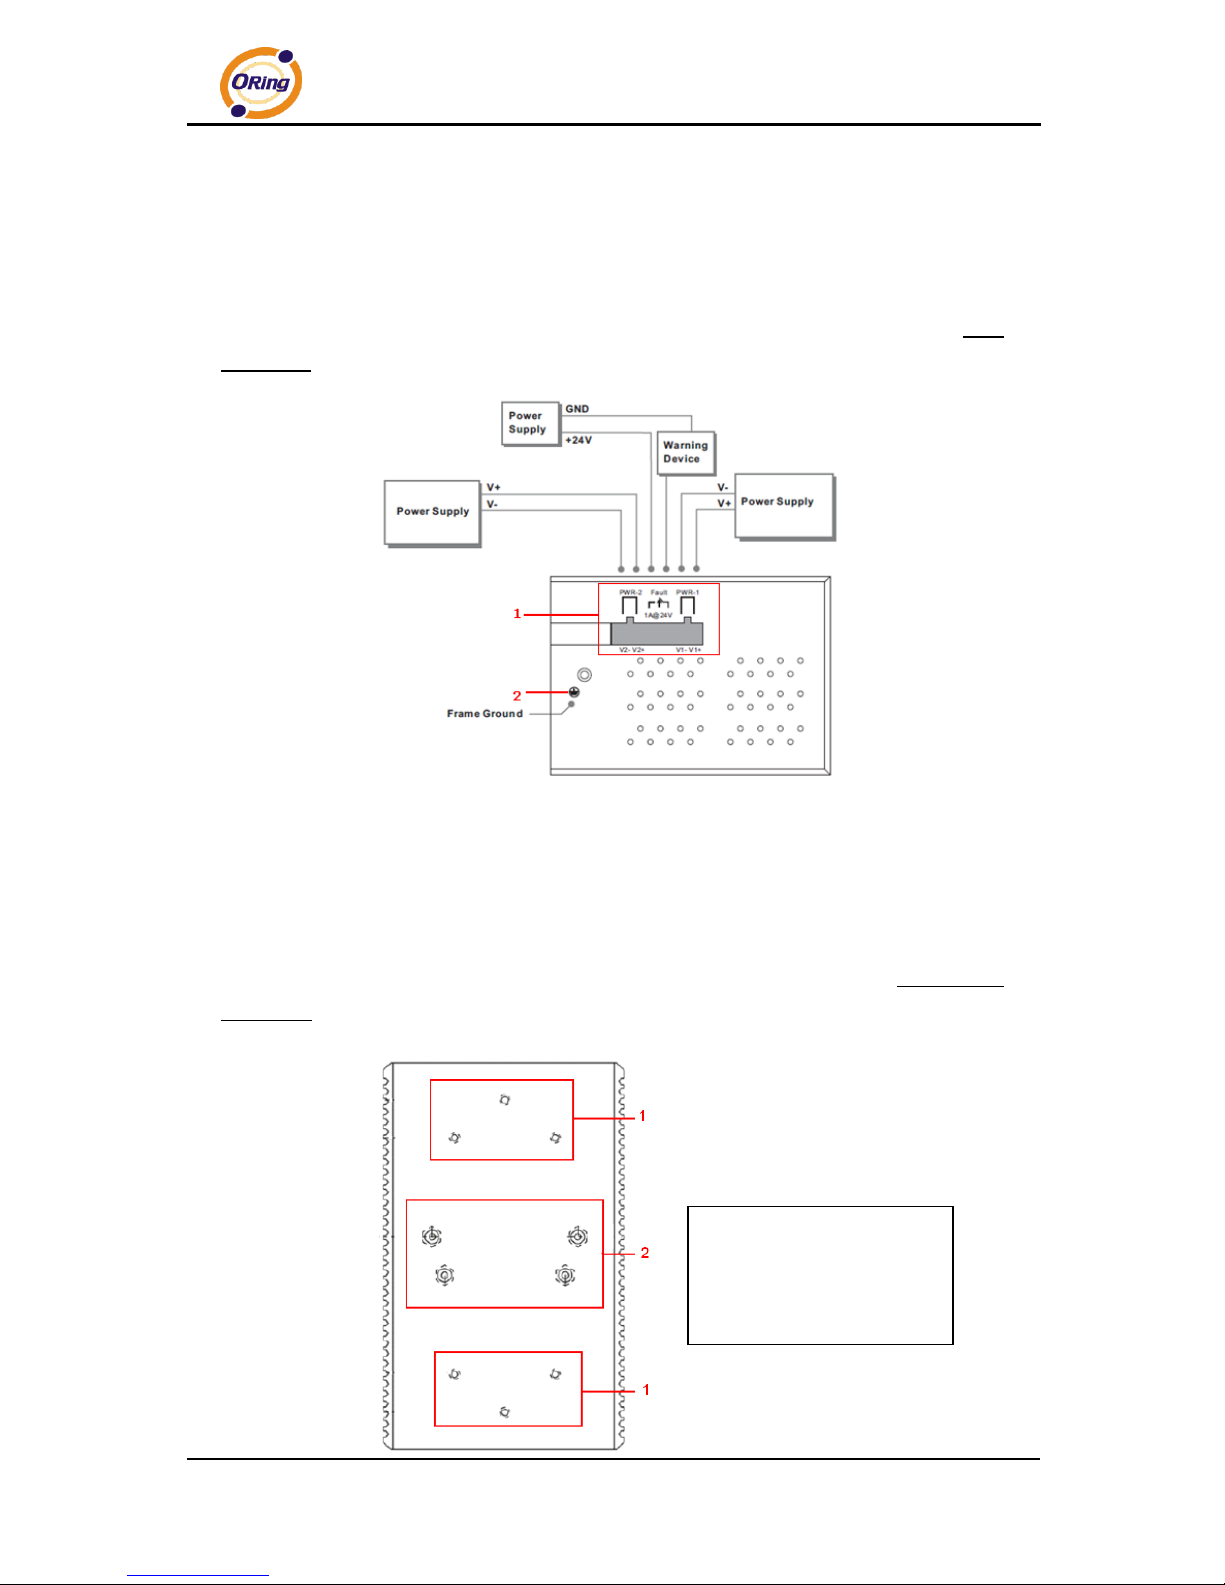
Below are the top panel components of the IGS-9844/9848GPF series:
1. Terminal blocks: PWR1, PWR2 (12-48V DC), Relay
2. Ground wire. For more information on how to ground the switch, please refer to 3.3.1
Grounding.
2.3 Rear Panel
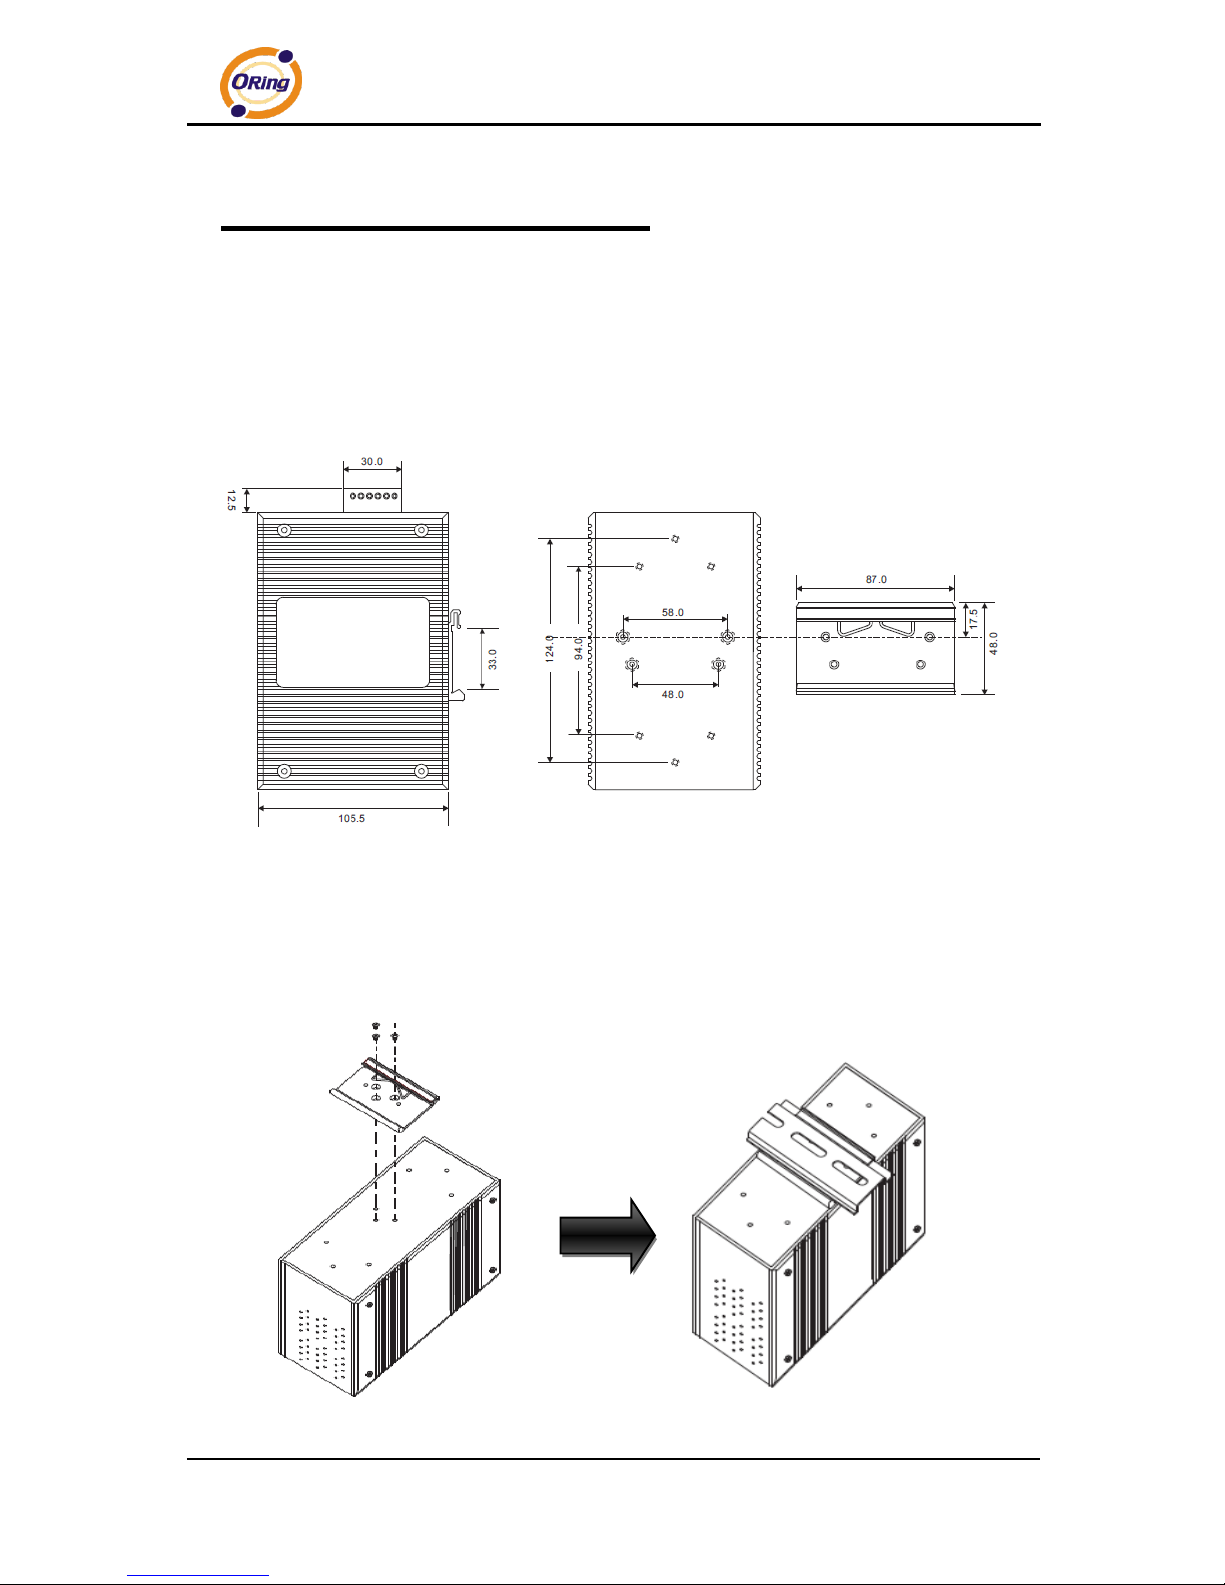
On the rear panel of the switch sit three sets of screw holes. The two sets placed in
triangular patterns on both ends of the rear panel are used for wall-mounting (red boxes in the
figure below) and the set of four holes in the middle are used for Din-rail installation (blue box
in the figure below). For more information on installation, please refer to 23.1 Din-rail
Installation.
1. Wall-mount screw
holes
2. Din-rail screw holes
Page 12
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
11
Hardware Installation
3.1 DIN-rail Installation
The device comes with a DIN-rail kit to allow you to fasten the switch to a DIN-rail in any
environments.
DIN-rail Kit Measurement
Installing the switch on the DIN-rail is easy. First, screw the Din-rail kit onto the back of the
switch, right in the middle of the back panel. Then slide the switch onto a DIN-rail from the
Din-rail kit and make sure the switch clicks into the rail firmly.
Page 13
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
12
3.2 Wall Mounting
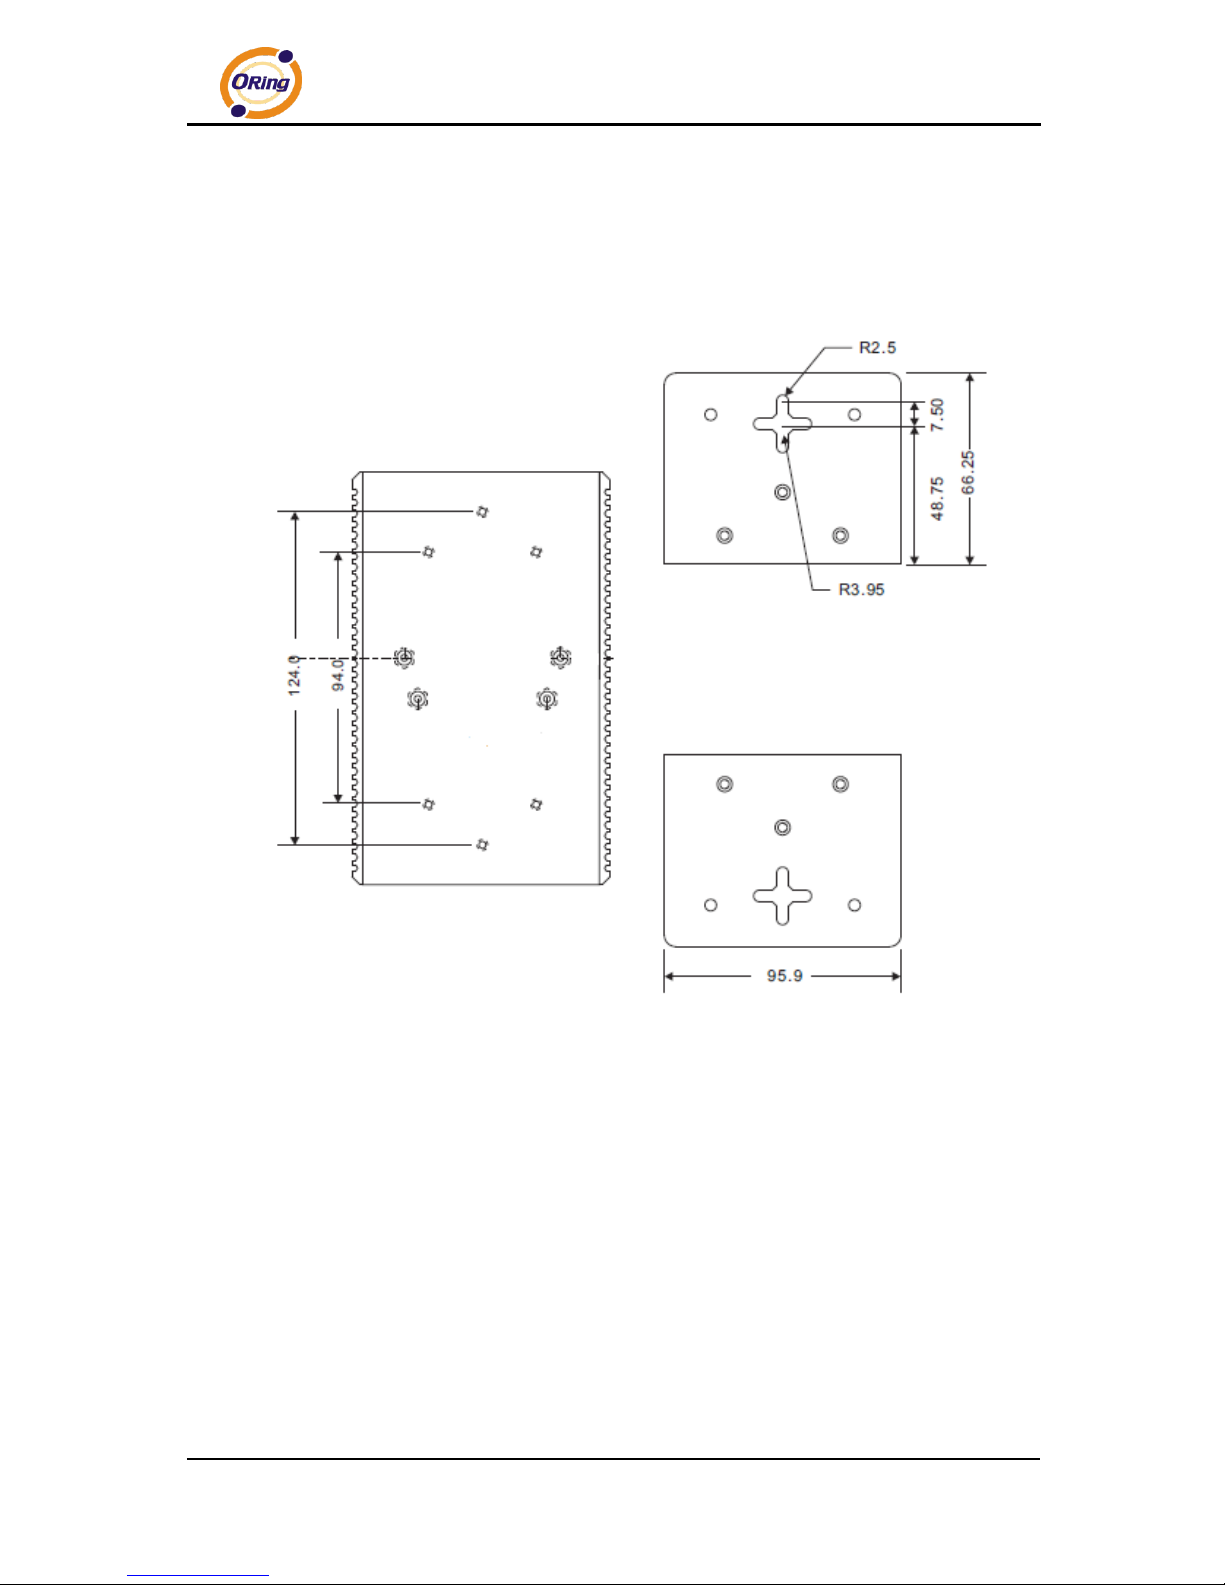
Besides Din-rail, the switch can be fixed to the wall via a wall mount panel, which can be found
in the package.
Wall-Mount Kit Measurement
To mount the switch onto the wall, follow the steps:
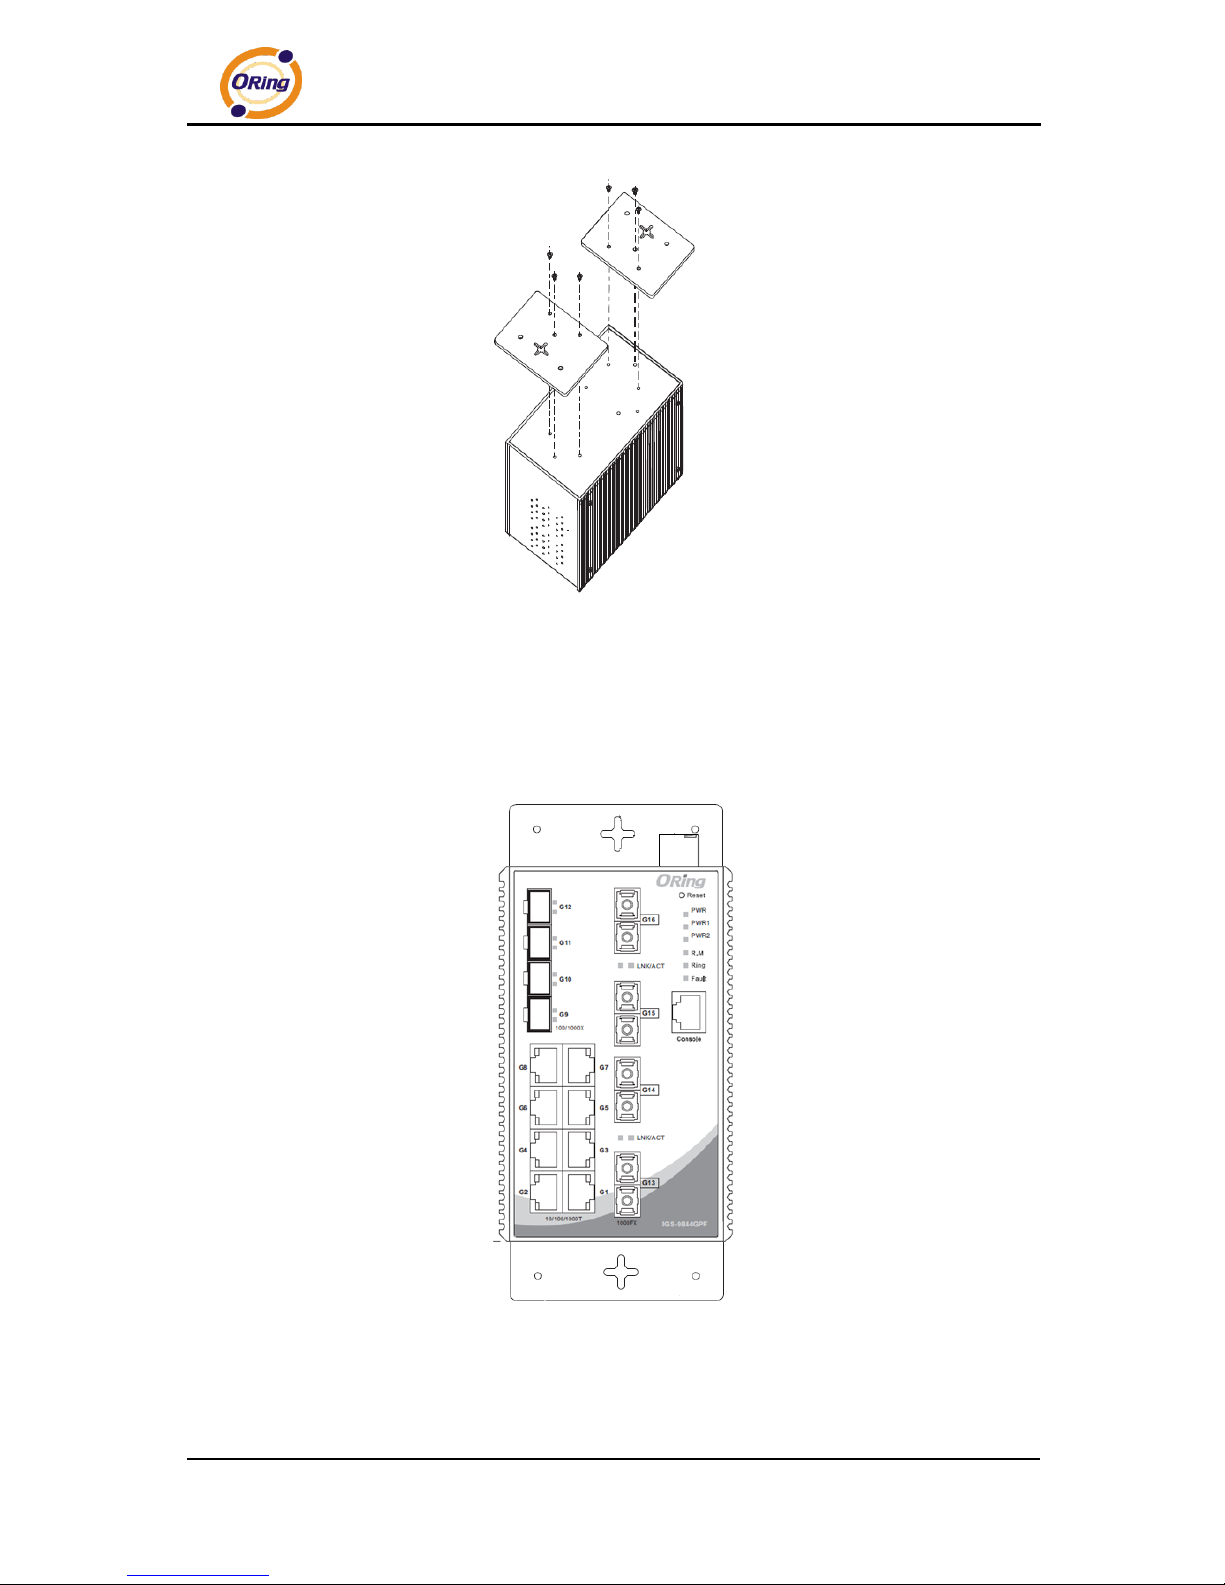
1. Screw the two pieces of wall-mount kits onto both ends of the rear panel of the switch. A
total of six screws are required, as shown below.
Page 14
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
13
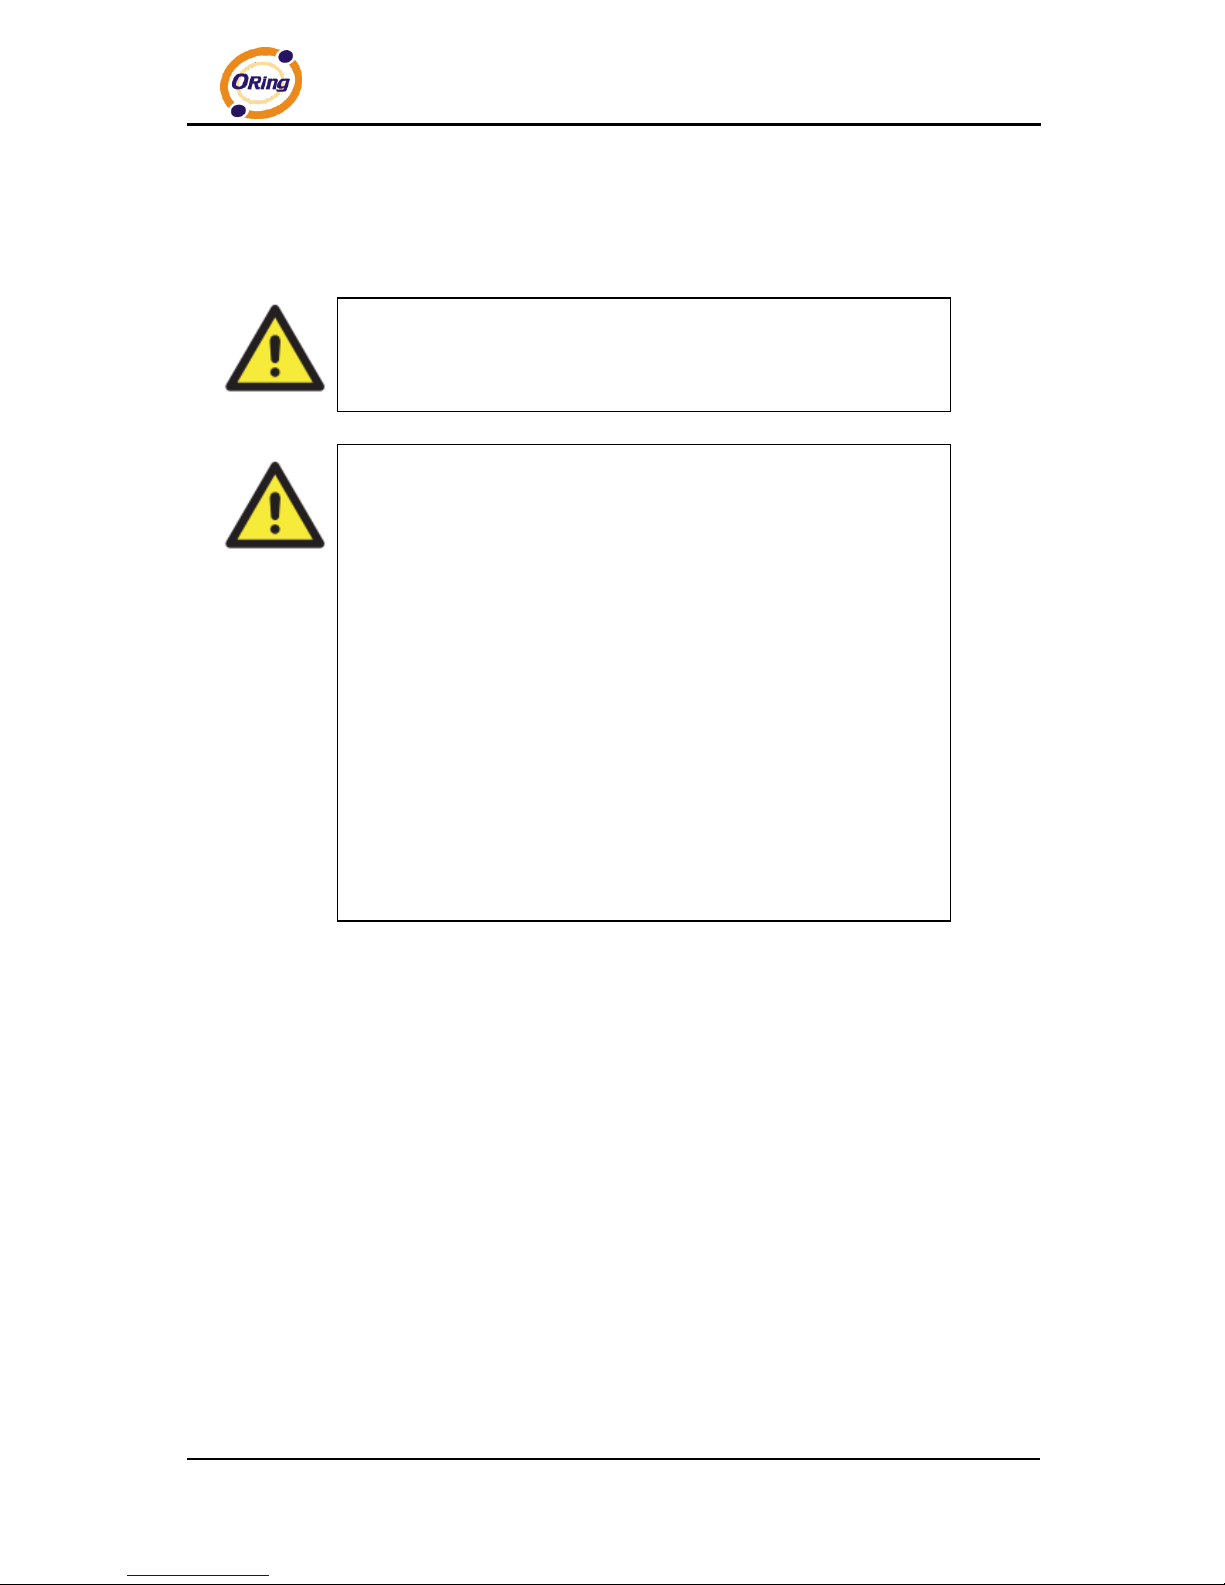
2. Use the switch, with wall mount plates attached, as a guide to mark the correct locations of
the four screws.
3. Insert four screw heads through the large parts of the keyhole-shaped apertures, and then
slide the switch downwards. Tighten the four screws for added stability.
Note: Instead of screwing the screws in all the way, leave about 2 mm to allow room for sliding
the wall mount panel between the wall and the screws.
Page 15
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
14
3.3 Wiring
3.3.1 Grounding
Grounding and wire routing help limit the effects of noise due to electromagnetic interference
(EMI). Run the ground connection from the ground screw to the grounding surface prior to
connecting devices.
3.3.2 Fault Relay
The two sets of relay contacts of the 6-pin terminal block connector are used to detect
user-configured events. The two wires attached to the fault contacts form an open circuit when
a user-configured when an event is triggered. If a user-configured event does not occur, the
fault circuit remains closed.
3.3.3 Redundant Power Inputs
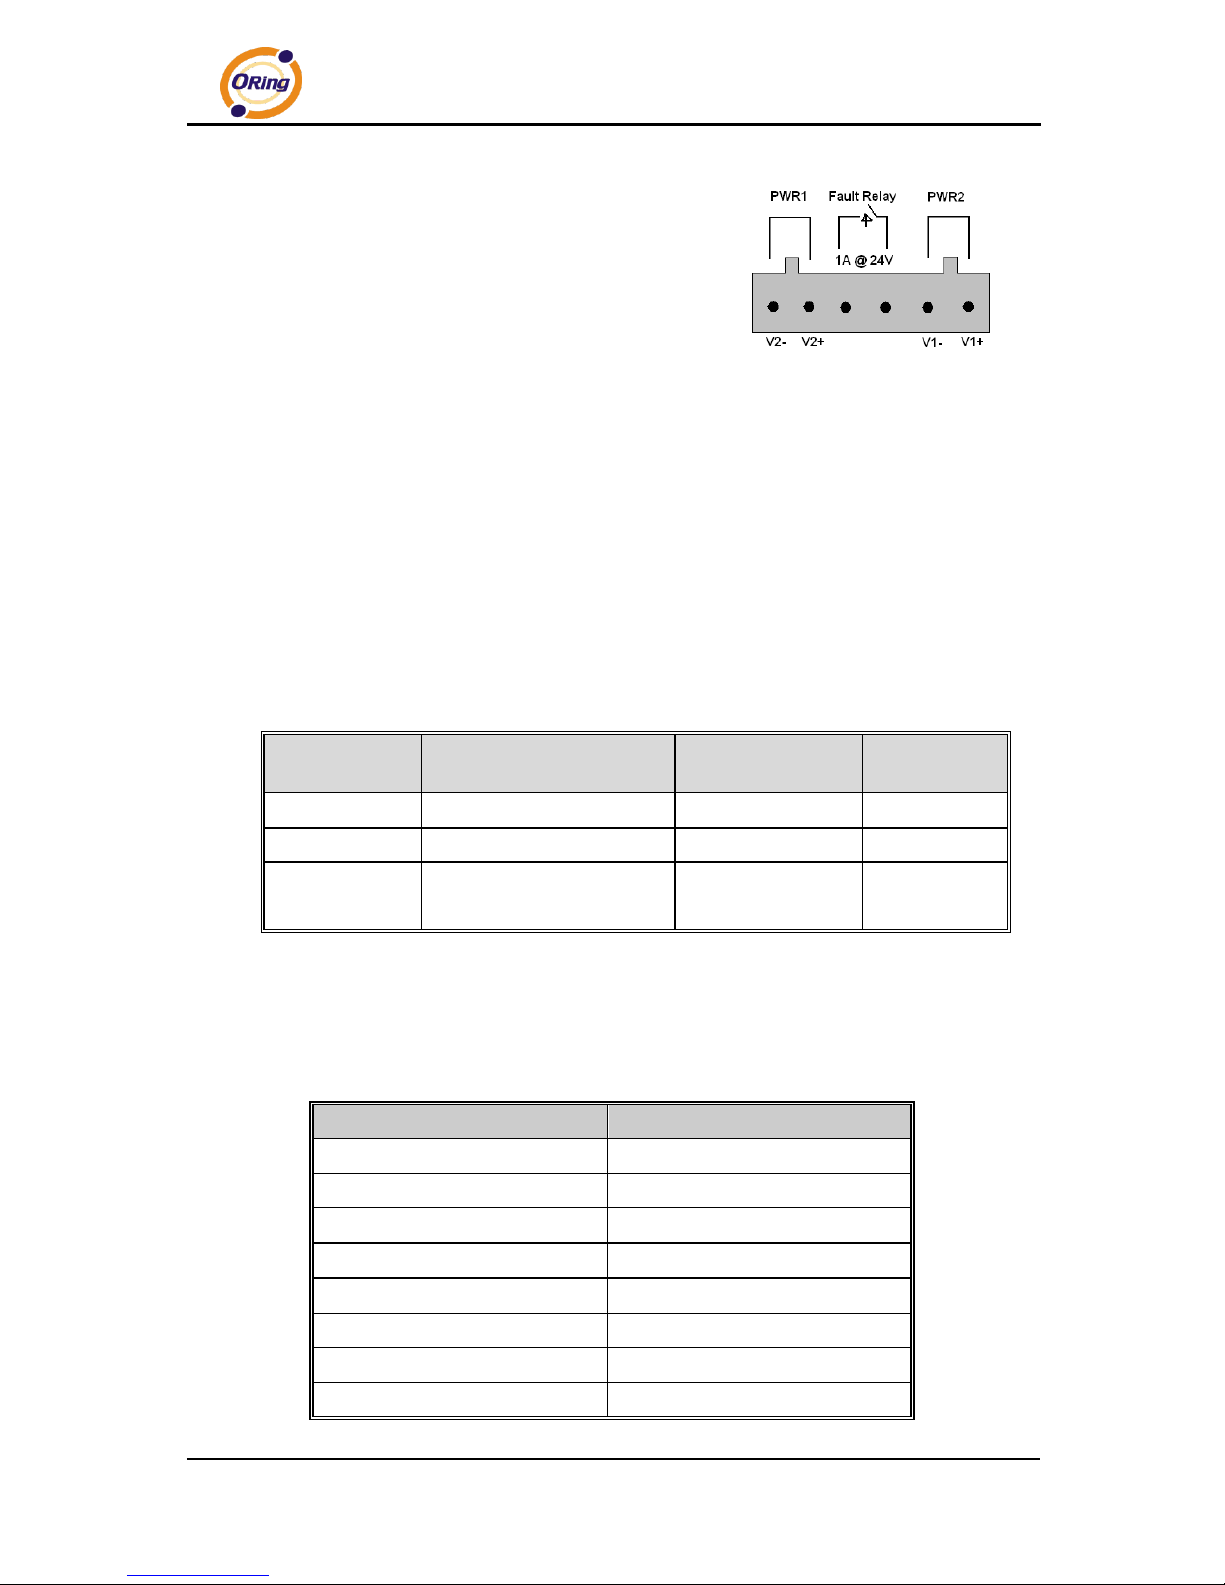
The switch has two sets of power inputs, power input 1 and power input 2. The top two
contacts and the bottom two contacts of the 6-pin terminal block connector on the switch‟s top
panel are used for the two digital inputs. Follow the steps below to wire redundant power
WARNING
Do not disconnect modules or wires unless power has been switched
off or the area is known to be non-hazardous. The devices may only
be connected to the supply voltage shown on the type plate.
ATTENTION
1. Be sure to disconnect the power cord before installing and/or
wiring your switches.
2. Calculate the maximum possible current in each power wire and
common wire. Observe all electrical codes dictating the maximum
current allowable for each wire size.
3. If the current goes above the maximum ratings, the wiring could
overheat, causing serious damage to your equipment.
4. Use separate paths to route wiring for power and devices. If power
wiring and device wiring paths must cross, make sure the wires
are perpendicular at the intersection point.
5. Do not run signal or communications wiring and power wiring
through the same wire conduit. To avoid interference, wires with
different signal characteristics should be routed separately.
6. You can use the type of signal transmitted through a wire to
determine which wires should be kept separate. The rule of thumb
is that wiring sharing similar electrical characteristics can be
bundled together
7. You should separate input wiring from output wiring
8. It is advised to label the wiring to all devices in the system
Page 16
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
15
inputs.
Step 1: insert the negative/positive wires into the V-/V+
terminals, respectively.
Step 2: to keep the DC wires from pulling loose, use a small
flat-blade screwdriver to tighten the wire-clamp screws on
the front of the terminal block connector.
3.4 Connection
3.4.1 Cables
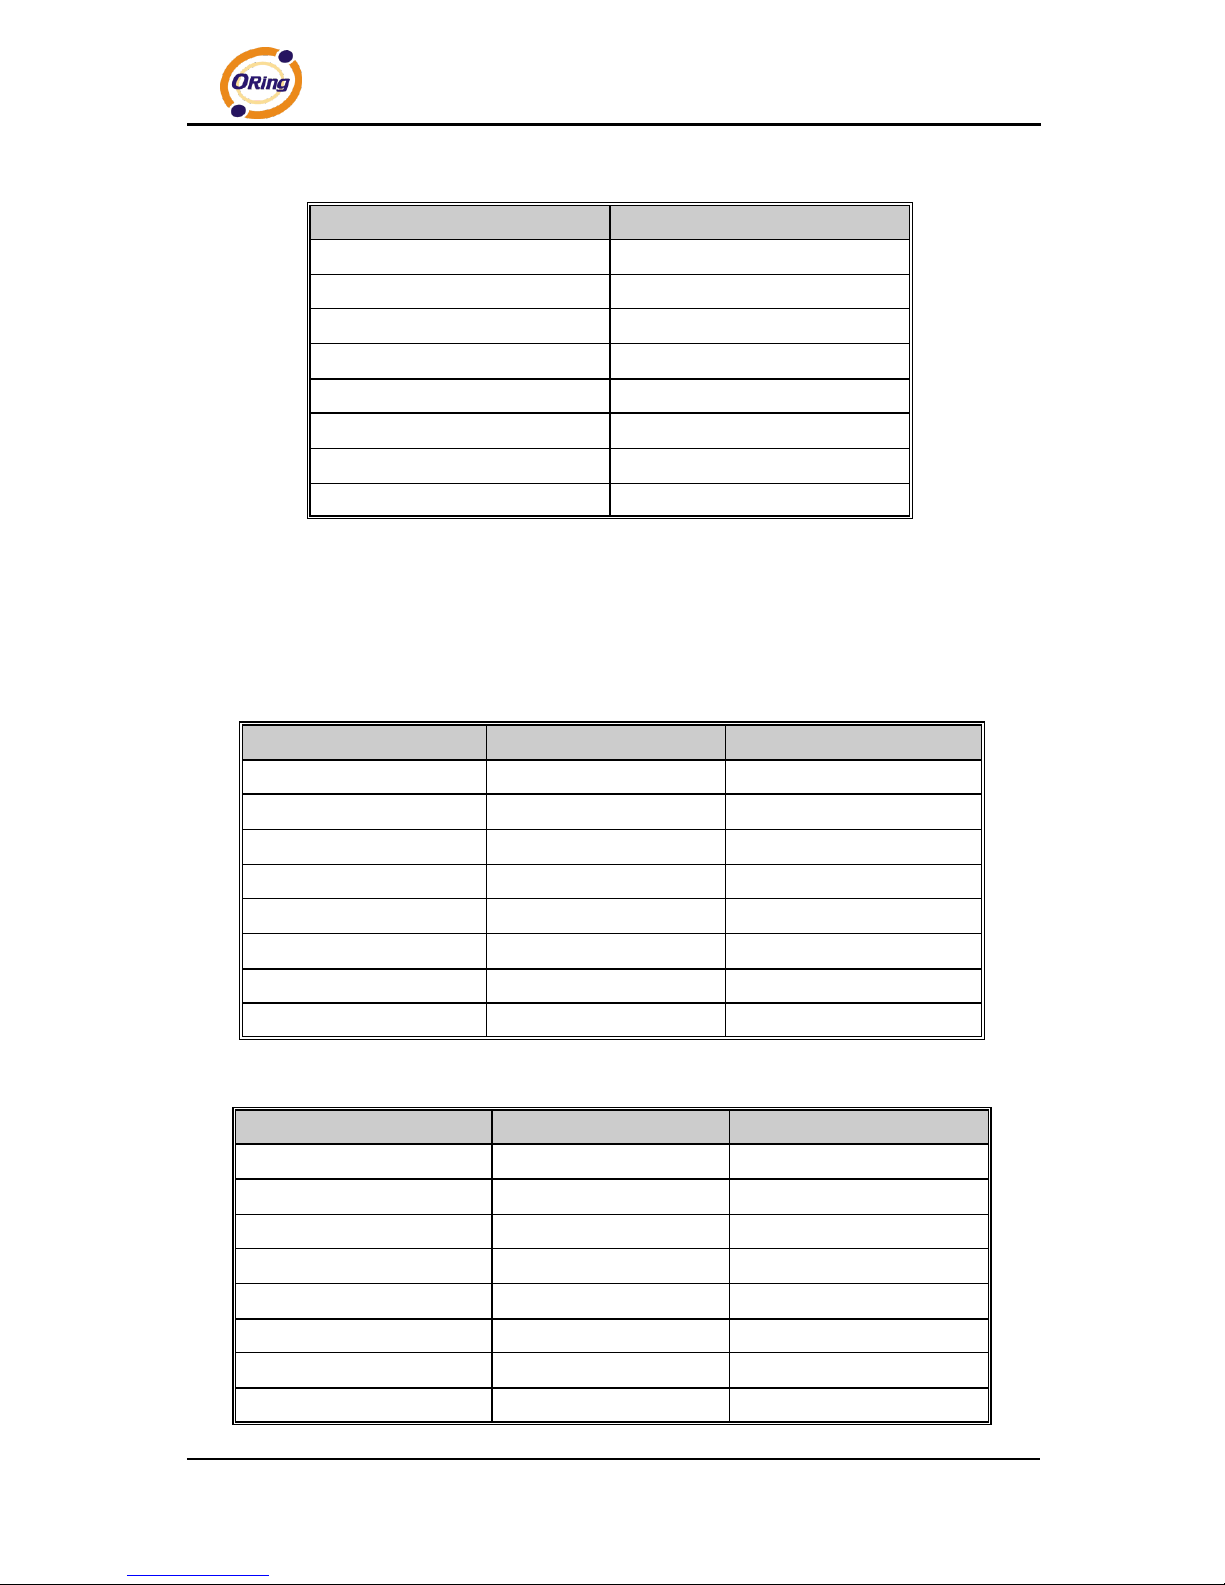
1000/100BASE-TX/10BASE-T Pin Assignments
The IGS-9844/9848GPF series have standard Ethernet ports. According to the link type, the
switch uses CAT 3, 4, 5,5e UTP cables to connect to any other network devices (PCs, servers,
switches, routers, or hubs). Please refer to the following table for cable specifications.
Cable Types and Specifications:
Cable
Type
Max. Length
Connector
10BASE-T
Cat. 3, 4, 5 100-ohm
UTP 100 m (328 ft)
RJ-45
100BASE-TX
Cat. 5 100-ohm UTP
UTP 100 m (328 ft)
RJ-45
1000BASE-TX
Cat. 5/Cat. 5e 100-ohm
UTP
UTP 100 m (328ft)
RJ-45
With 10/100/1000Base-T(X) cables, pins 1 and 2 are used for transmitting data, and pins 3 and
6 are used for receiving data.
10/100 Base-T(X) RJ-45 Pin Assignments:
Pin Number
Assignment
1
TD+ 2 TD-
3
RD+
4
Not used
5
Not used
6
RD-
7
Not used
8
Not used
Page 17
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
16
1000 Base-T RJ-45 Pin Assignments:
Pin Number
Assignment 1 BI_DA+
2
BI_DA-
3
BI_DB+
4
BI_DC+
5
BI_DC-
6
BI_DB-
7
BI_DD+
8
BI_DD-
The IGS-9844GP series switches support auto MDI/MDI-X operation. You can use a cable to
connect the switch to a PC. The table below shows the 10/100Base-T(X) MDI and MDI-X port
pin outs.
10/100 Base-T(X) MDI/MDI-X Pin Assignments:
Pin Number
MDI port
MDI-X port
1
TD+(transmit)
RD+(receive)
2
TD-(transmit)
RD-(receive)
3
RD+(receive)
TD+(transmit)
4
Not used
Not used
5
Not used
Not used
6
RD-(receive)
TD-(transmit)
7
Not used
Not used
8
Not used
Not used
1000Base-T(X) MDI/MDI-X Pin Assignments:
Pin Number
MDI port
MDI-X port 1 BI_DA+
BI_DB+
2
BI_DA-
BI_DB-
3
BI_DB+
BI_DA+
4
BI_DC+
BI_DD+
5
BI_DC-
BI_DD-
6
BI_DB-
BI_DA-
7
BI_DD+
BI_DC+
8
BI_DD-
BI_DC-
Page 18
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
17
Note: “+” and “-” signs represent the polarity of the wires that make up each wire pair.
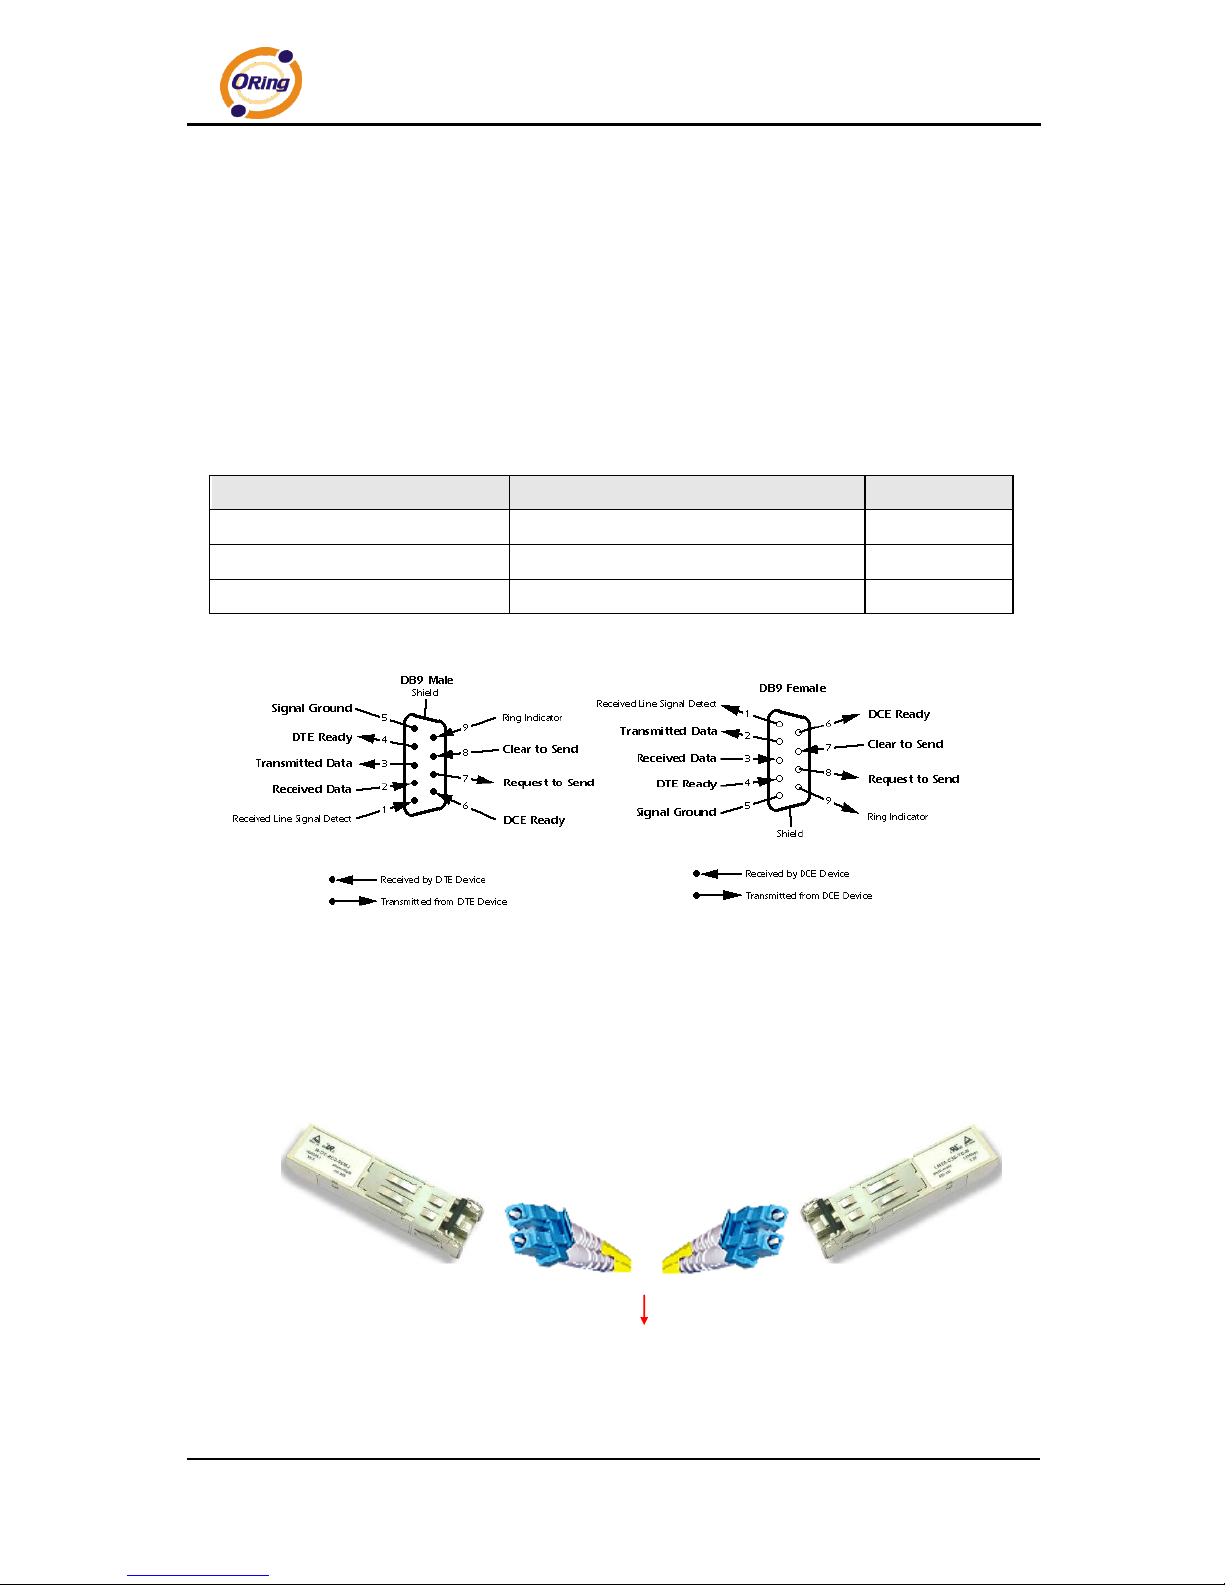
RS-232 console port wiring
The IGS-9844/9848GPF series can be managed via console ports using a RS-232 cable
which can be found in the package. You can connect the port to a PC via the RS-232 cable
with a DB-9 female connector. The DB-9 female connector of the RS-232 cable should be
connected the PC while the other end of the cable (RJ-45 connector) should be connected to
the console port of the switch.
PC pin out (male) assignment
RS-232 with DB9 female connector
DB9 to RJ 45
Pin #2 RD
Pin #2 TD
Pin #2
Pin #3 TD
Pin #3 RD
Pin #3
Pin #5 GD
Pin #5 GD
Pin #5
3.4.2 SFP
The switch comes with fiber optical ports that can connect to other devices using SFP modules.
The fiber optical ports are in multi-mode and single-mode with LC connectors. Please
remember that the TX port of Switch A should be connected to the RX port of Switch B.
Fiber cord
Switch A
Switch B
Page 19
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
18
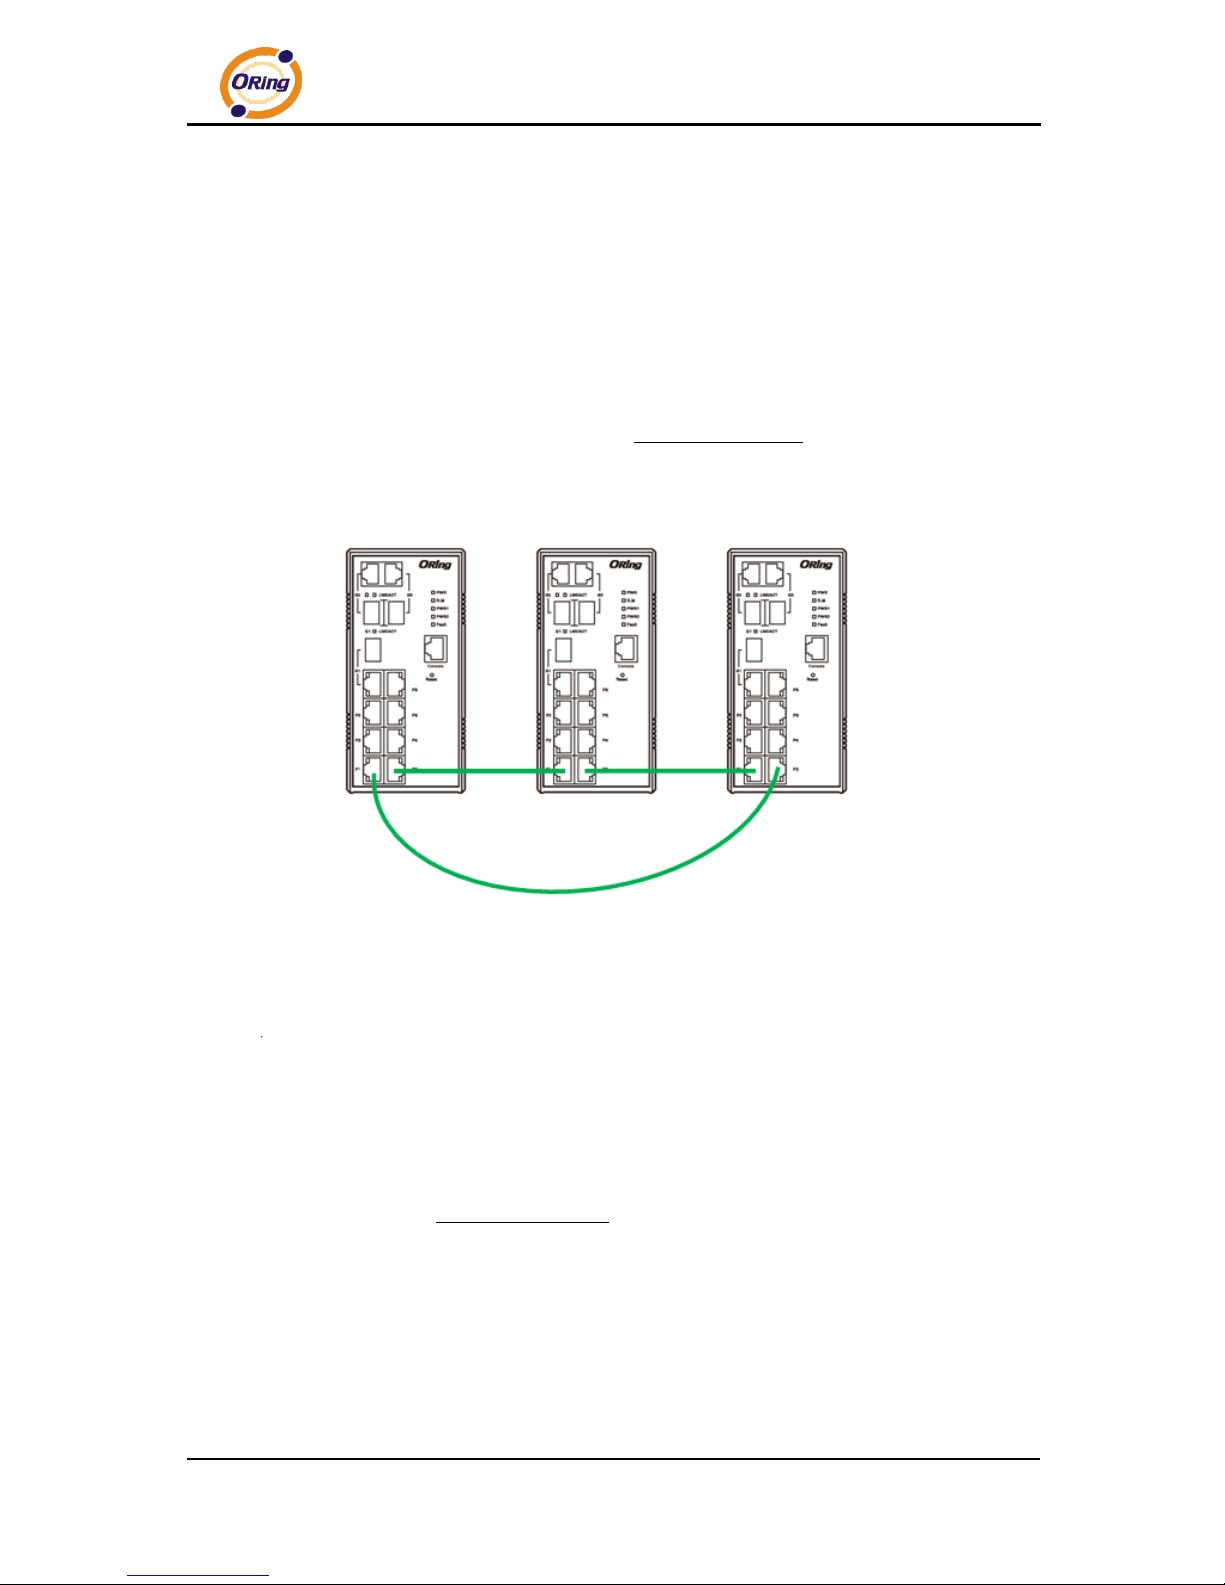
3.4.3 O-Ring/O-Chain
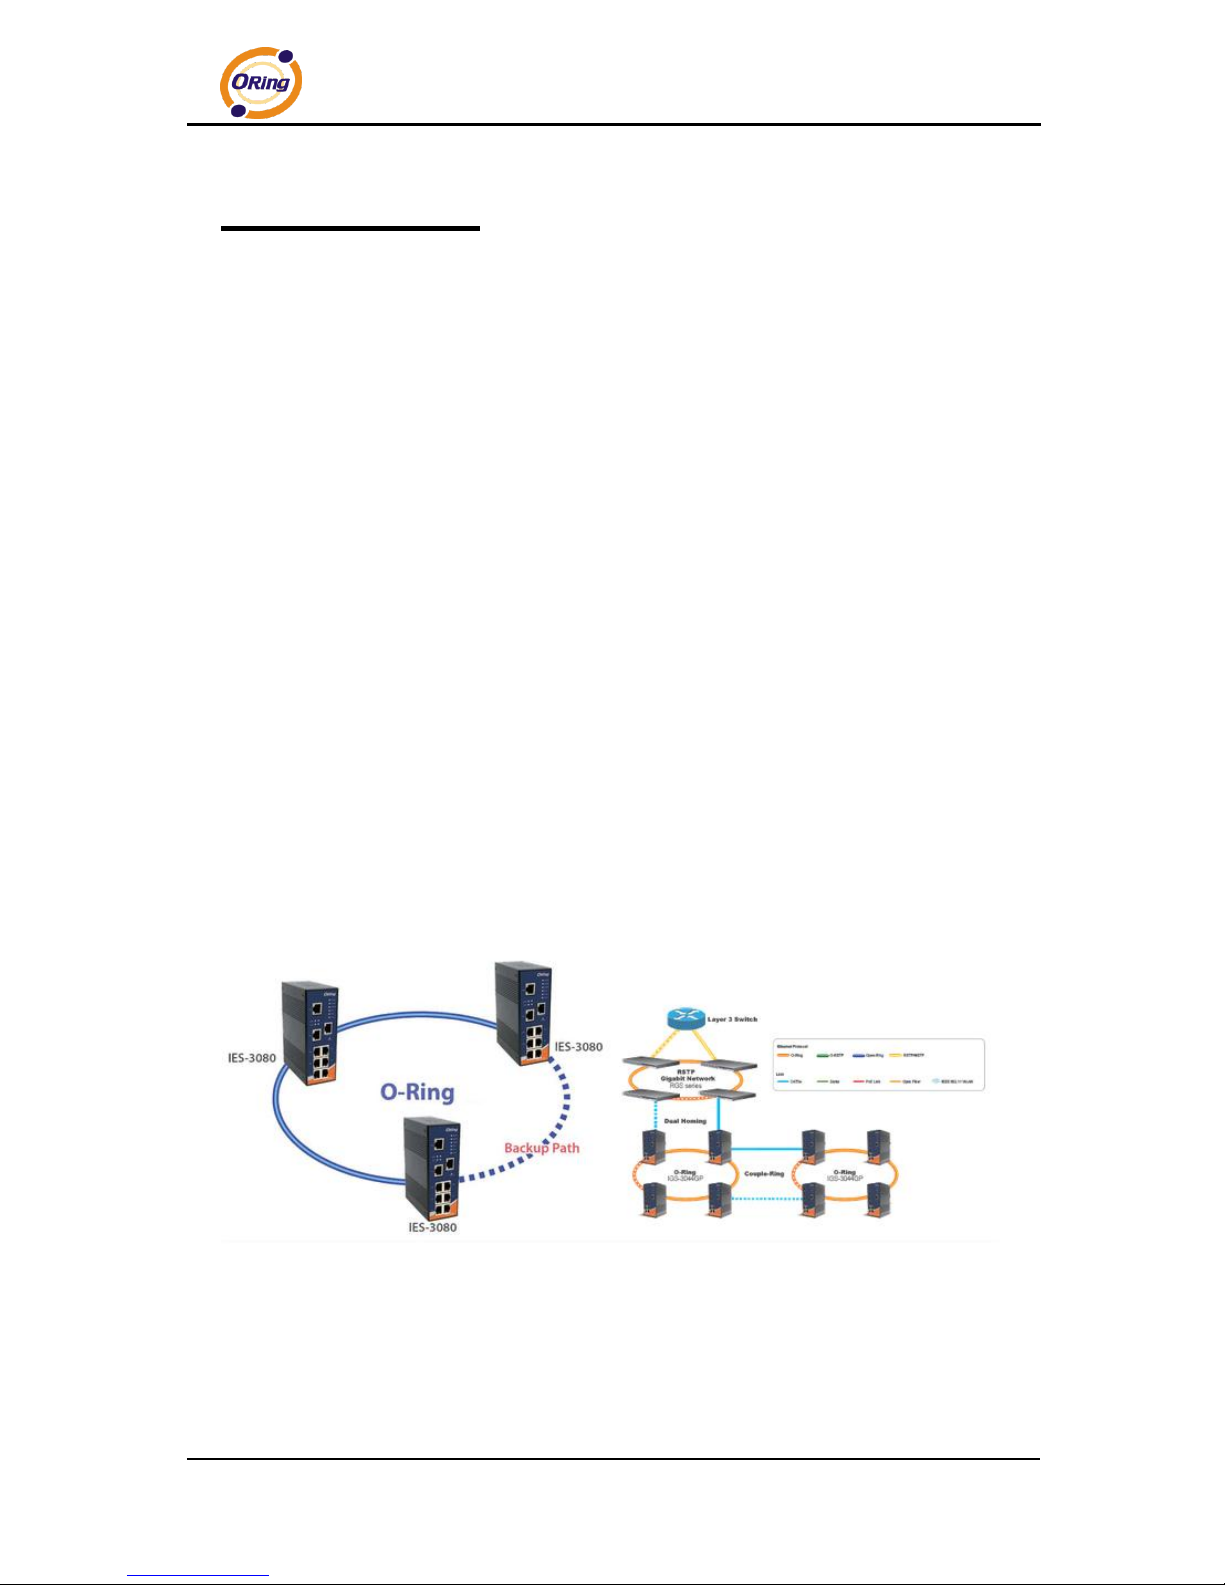
O-Ring
You can connect three or more switches to form a ring topology to gain network redundancy
capabilities through the following steps.
1. Connect each switch to form a daisy chain using an Ethernet cable.
2. Set one of the connected switches to be the master and make sure the port setting of each
connected switch on the management page corresponds to the physical ports connected. For
information about the port setting, please refer to 4.1.2 Configurations.
3. Connect the last switch to the first switch to form a ring topology.
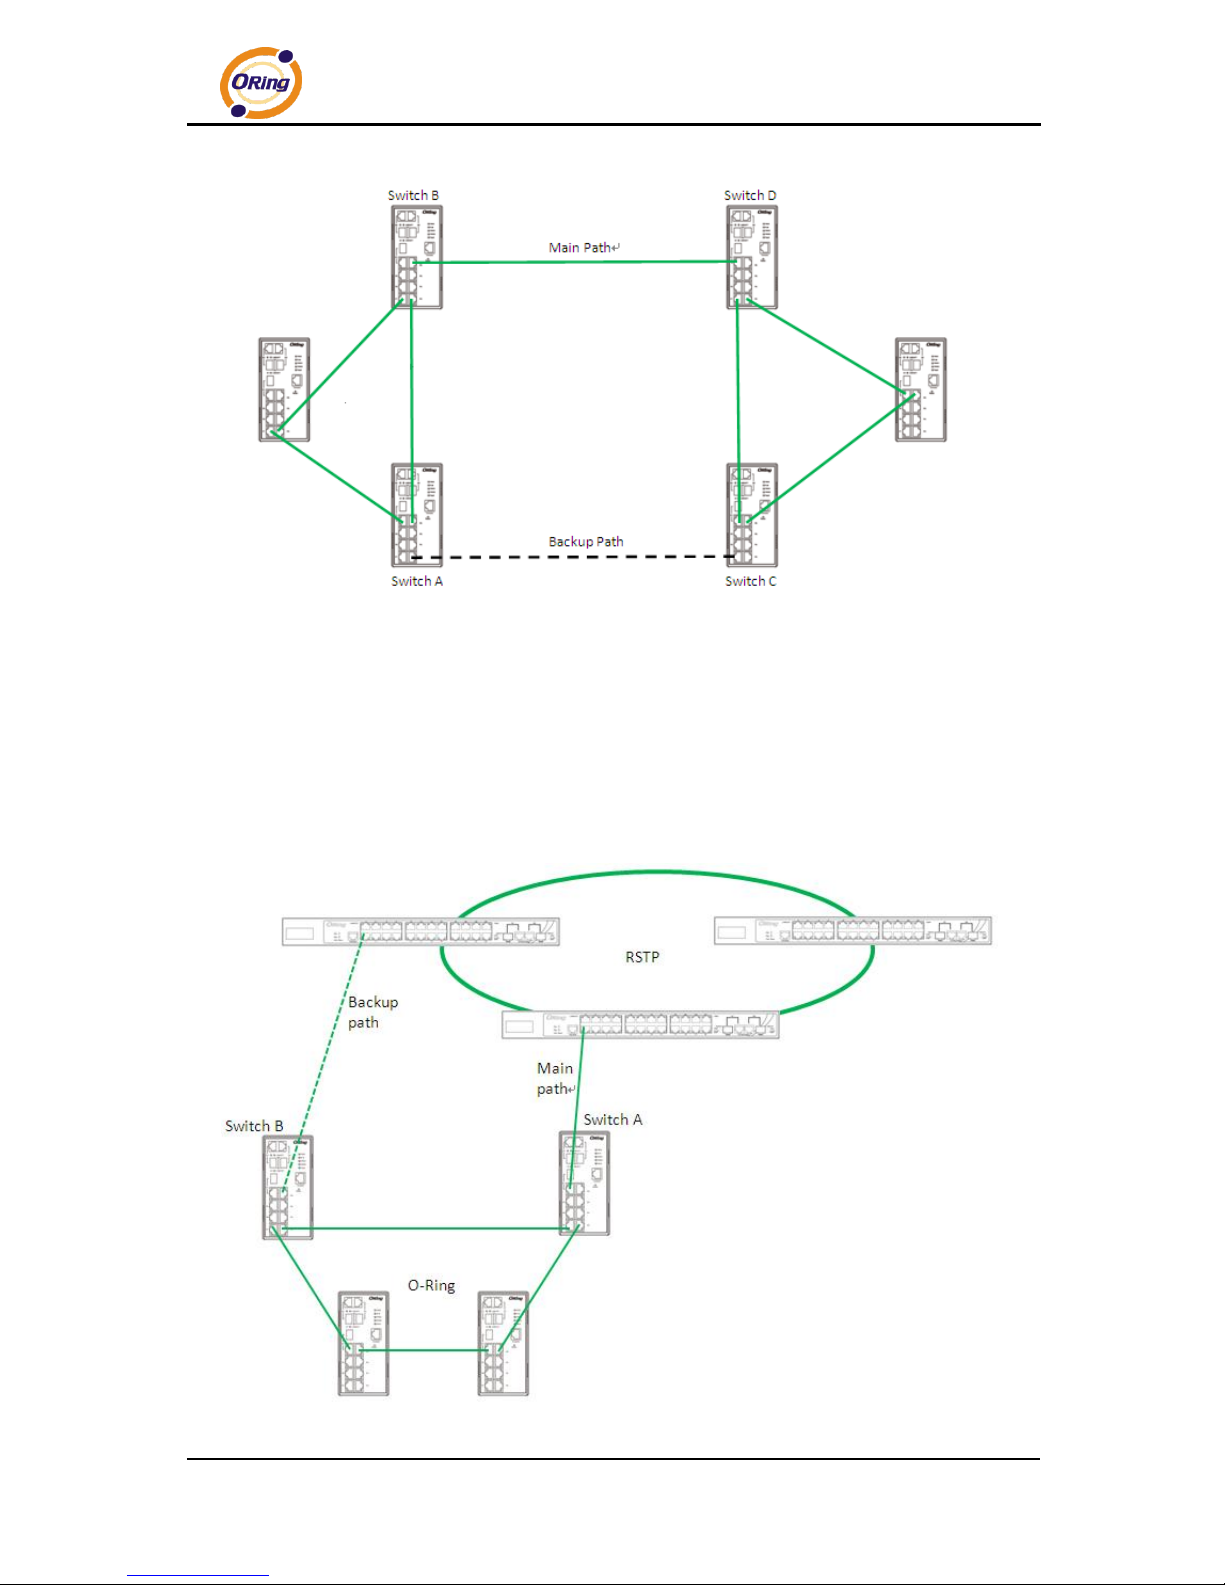
Coupling Ring
If you already have two O-Ring topologies and would like to connect the rings, you can form
them into a couping ring. All you need to do is select two switches from each ring to be
connected, for example, switch A and B from Ring 1 and switch C and D from ring 2. Decide
which port on each switch to be used as the coupling port and then link them together, for
example, port 1 of switch A to port 2 of switch C and port 1 of switch B to port 2 of switch D.
Then, enable Coupling Ring option by checking the checkbox on the management page and
select the coupling ring in correspondance to the connected port. For more inforamtion on port
setting, please refer to 4.1.2 Configurations. Once the setting is completed, one of the
connections will act as the main path while the other will act as the backup path.
Page 20
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
19
Dual Homing
If you want to connect your ring topology to a RSTP network environment, you can use dual
homing. Choose two switches (Switch A & B) from the ring for connecting to the switches in the
RSTP network (core switches). The connection of one of the switches (Switch A or B) will act
as the primary path, while the other will act as the backup path that is activated when the
primary path connection fails.
Page 21
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
20
O-Chain
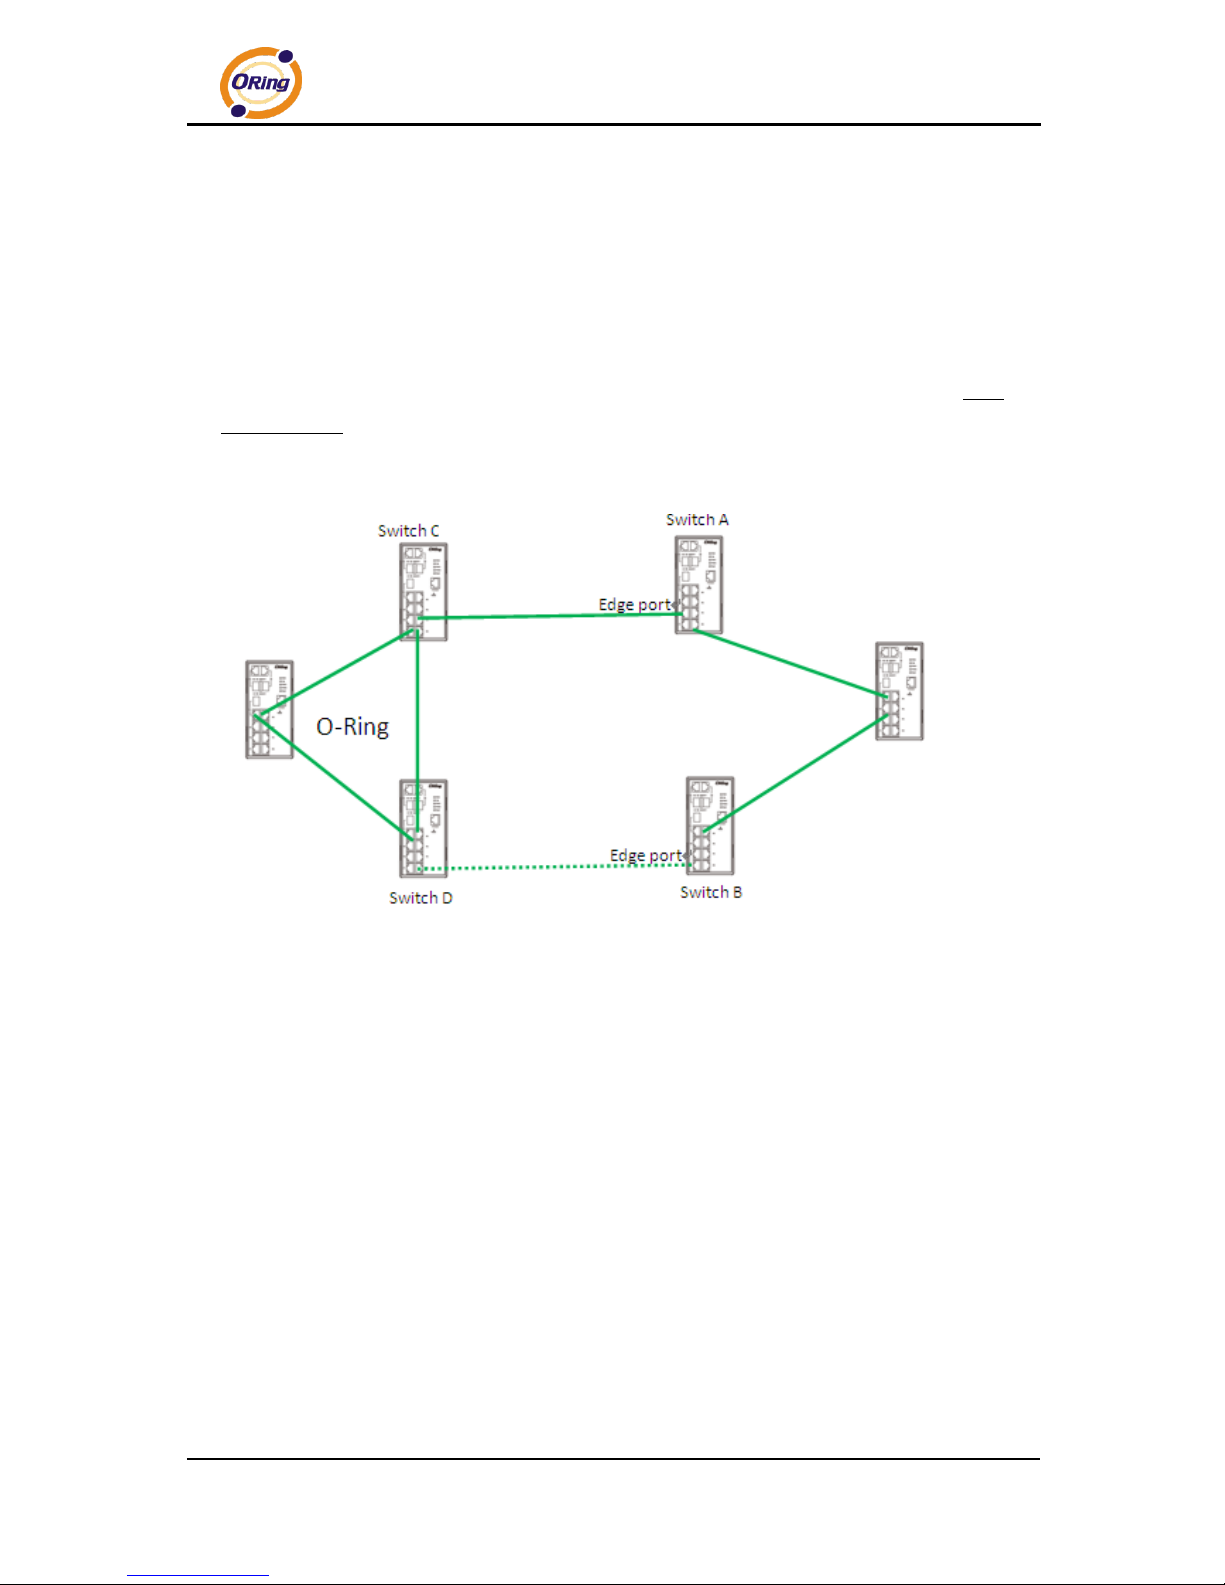
When connecting multiple O-Rings to meet your expansion demand, you can create an
O-Chain topology through the following steps.
1. Select two switches from the chain (Switch A & B) that you want to connect to the O-Ring
and connect them to the switches in the ring (Switch C & D).
2. In correspondence to the port connected to the ring, configure an edge port for both of the
connected switches in the chain by checking the box in the management page (see 4.1.2
Configurations).
3. Once the setting is completed, one of the connections will act as the main path, and the
ohter as the back up path.
Page 22
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
21
Redundancy
Redundancy for minimized system downtime is one of the most important concerns for
industrial networking devices. Hence, ORing has developed proprietary redundancy
technologies including O-Ring and Open-Ring featuring faster recovery time than existing
redundancy technologies widely used in commercial applications, such as STP, RSTP, and
MSTP. ORing‟s proprietary redundancy technologies not only support different networking
topologies, but also assure the reliability of the network.
4.1 O-Ring
4.1.1 Introduction
O-Ring is ORing's proprietary redundant ring technology, with recovery time of less than 30
milliseconds (in full-duplex Gigabit operation) or 10 milliseconds (in full-duplex Fast Ethernet
operation) and up to 250 nodes. The ring protocols identify one switch as the master of the
network, and then automatically block packets from traveling through any of the network‟s
redundant loops. In the event that one branch of the ring gets disconnected from the rest of the
network, the protocol automatically readjusts the ring so that the part of the network that was
disconnected can reestablish contact with the rest of the network. The O-Ring redundant ring
technology can protect mission-critical applications from network interruptions or temporary
malfunction with its fast recover technology.
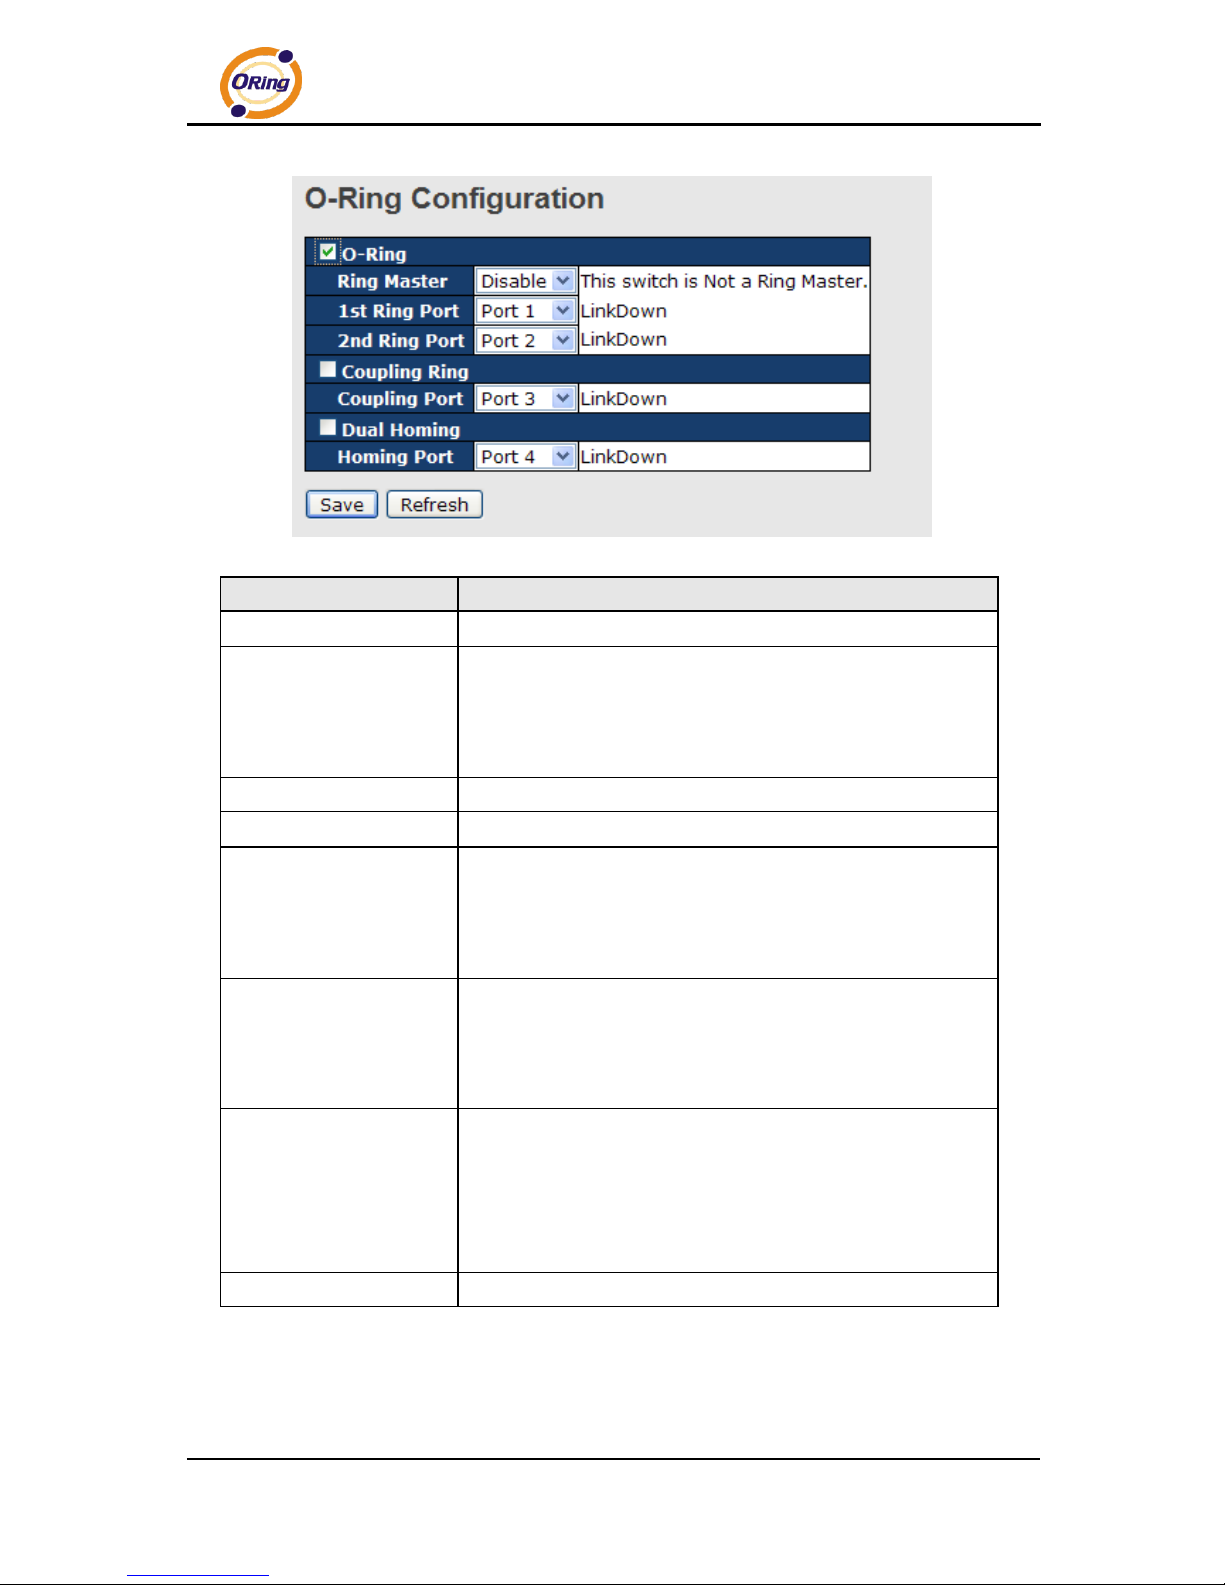
4.1.2 Configurations
O-Ring supports three ring topologies: Ring Master, Coupling Ring, and Dual Homing. You
can configure the settings in the interface below.
Page 23
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
22
Label
Description
Redundant Ring
Check to enable O-Ring topology.
Ring Master
Only one ring master is allowed in a ring. However, if more
than one switches are set to enable Ring Master, the switch
with the lowest MAC address will be the active ring master and
the others will be backup masters.
1st Ring Port
The primary port when the switch is ring master
2nd Ring Port
The backup port when the switch is ring master
Coupling Ring
Check to enable Coupling Ring. Coupling Ring can divide a
big ring into two smaller rings to avoid network topology
changes affecting all switches. It is a good method for
connecting two rings.
Coupling Port
Ports for connecting multiple rings. A coupling ring needs four
switches to build an active and a backup link.
Links formed by the coupling ports will run in active/backup
mode.
Dual Homing
Check to enable Dual Homing. When Dual Homing is
enabled, the ring will be connected to normal switches through
two RSTP links (ex: backbone Switch). The two links work in
active/backup mode, and connect each ring to the normal
switches in RSTP mode.
Apply
Click to apply the configurations.
Note: due to heavy computing loading, setting one switch as ring master and coupling ring at
the same time is not recommended.
Page 24
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
23
4.2 O-Chain
4.2.1 Introduction
O-Chain is ORing‟s revolutionary network redundancy technology which enhances network
redundancy for any backbone networks, providing ease-of-use and maximum fault-recovery
swiftness, flexibility, compatibility, and cost-effectiveness in a set of network redundancy
topologies. The self-healing Ethernet technology designed for distributed and complex
industrial networks enables the network to recover in less than 30 milliseconds (in full-duplex
Gigabit operation) or 10 milliseconds (in full-duplex Fast Ethernet operation) for up to 250
switches if at any time a segment of the chain fails.
O-Chain allows multiple redundant rings of different redundancy protocols to join and function
together as a large and the most robust network topologies. It can create multiple redundant
networks beyond the limitations of current redundant ring technologies.
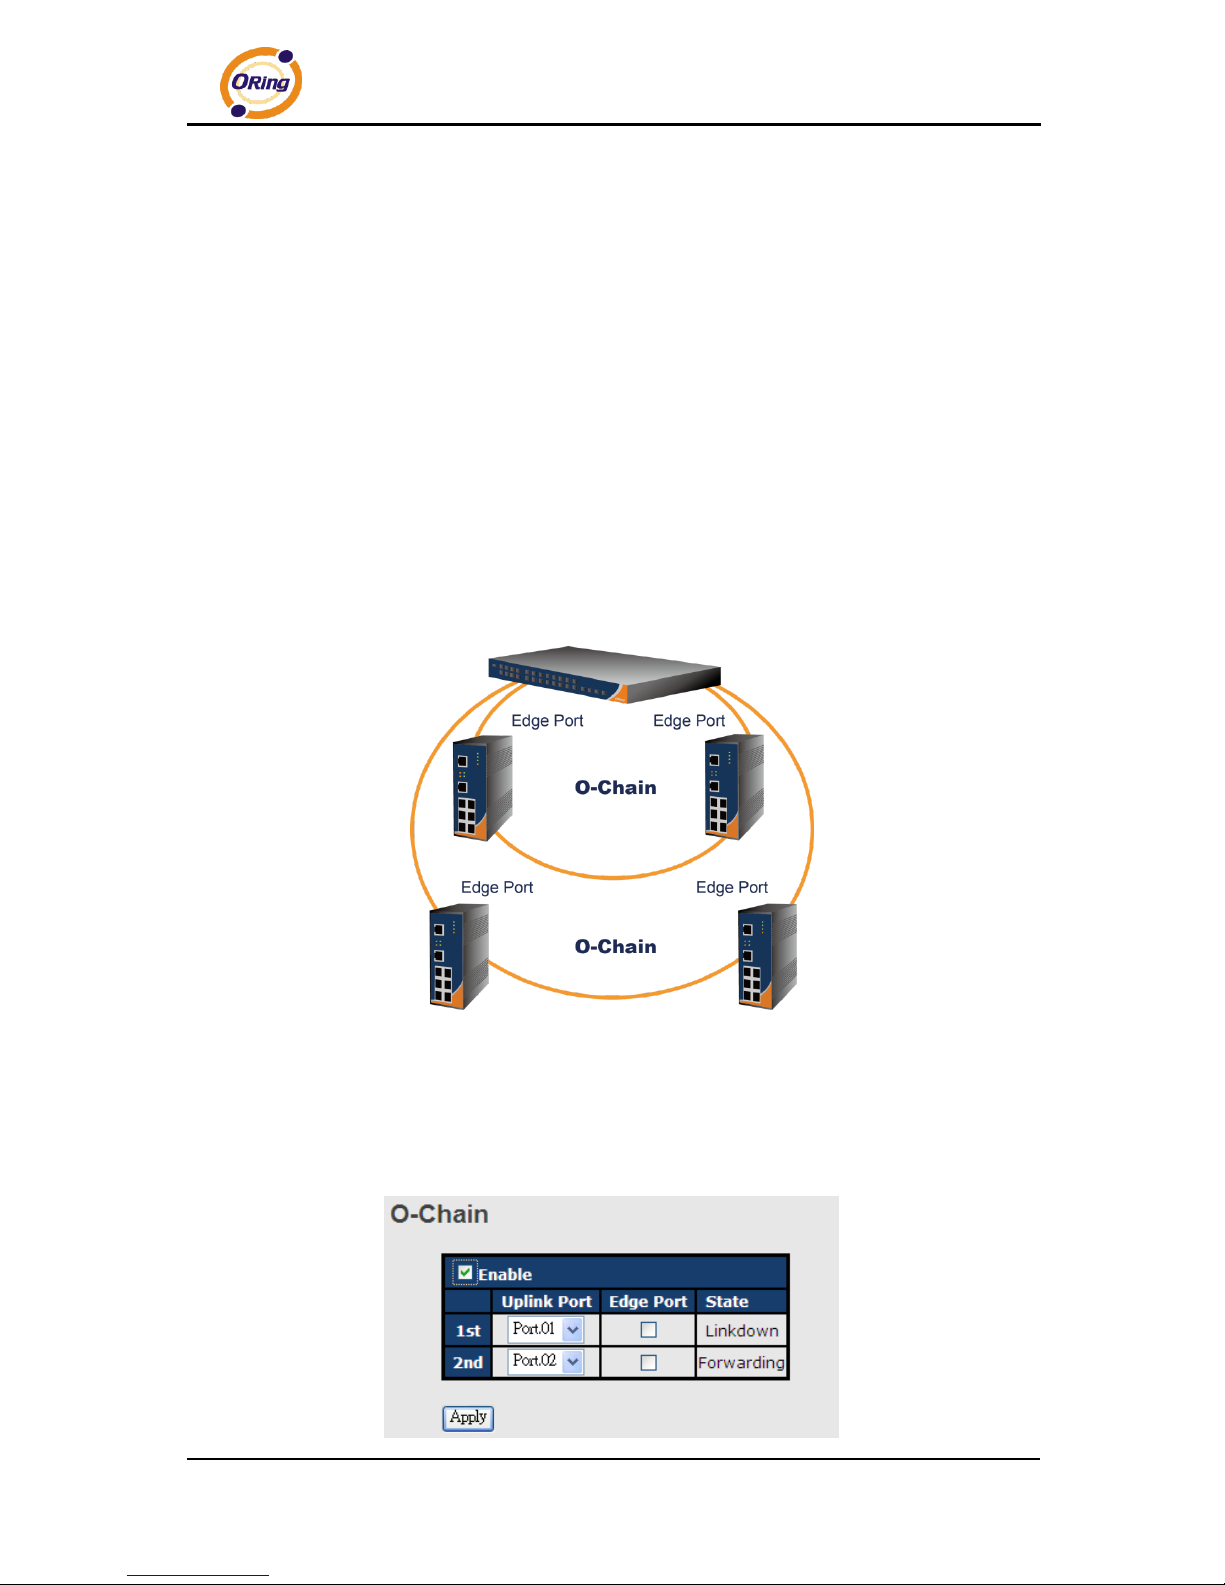
4.2.2 Configurations
O-Chain is very easy to configure and manage. Only one edge port of the edge switch needs
to be defined. Other switches beside them just need to have O-Chain enabled.
Page 25
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
24
Label
Description
Enable
Check to enable O-Chain function
1st Ring Port
The first port connecting to the ring
2nd Ring Port
The second port connecting to the ring
Edge Port
An O-Chain topology must begin with edge ports. The ports with a
smaller switch MAC address will serve as the backup link and RM
LED will light up.
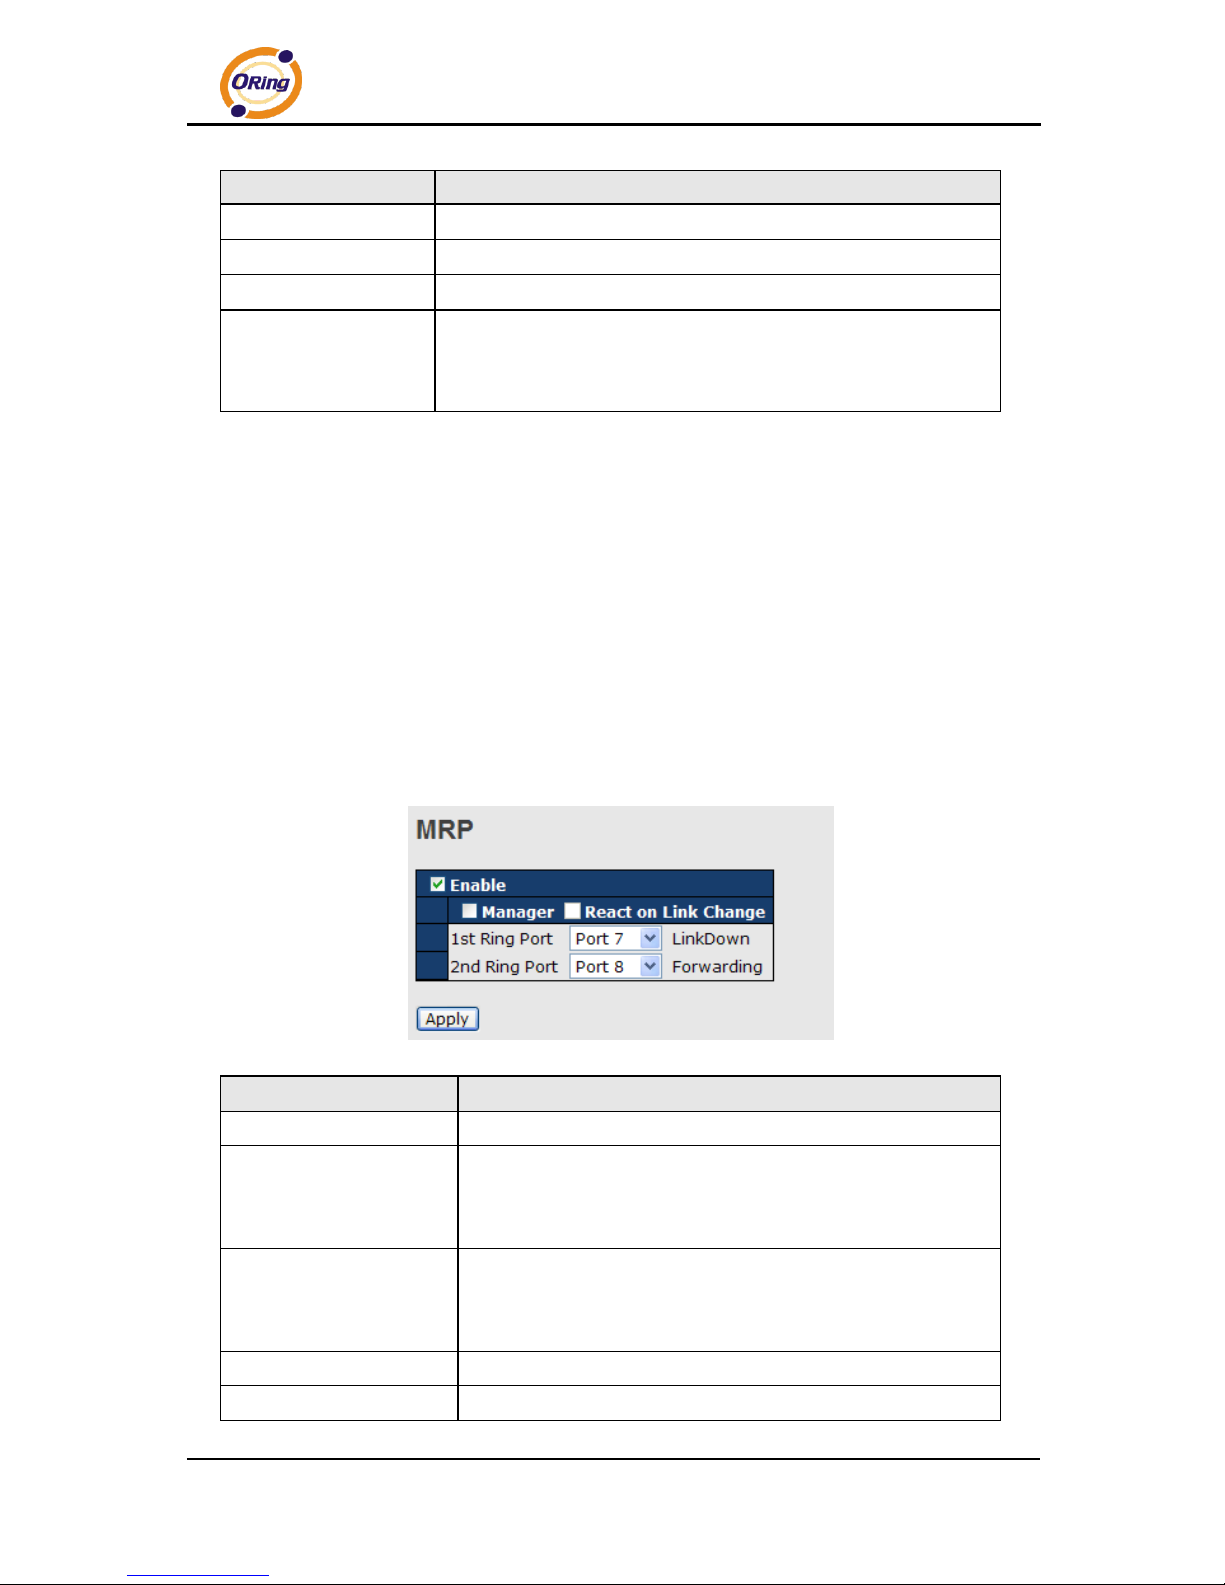
4.3 MRP
4.3.1 Introduction
MRP (Media Redundancy Protocol) is an industry standard for high-availability
Ethernet networks. MRP allowing Ethernet switches in ring configuration to recover from
failure rapidly to ensure seamless data transmission. A MRP ring (IEC 62439) can support up
to 50 devices and will enable a back-up link in 80ms (adjustable to max. 200ms/500ms).
4.3.2 Configurations
Label
Description
Enable
Enables the MRP function
Manager
Every MRP topology needs a MRP manager. One MRP
topology can only have a Manager. If two or more switches are
set to be Manager, the MRP topology will fail.
React on Link Change
(Advanced mode)
Faster mode. Enabling this function will cause MRP topology to
converge more rapidly. This function only can be set in MRP
manager switch.
1st Ring Port
Chooses the port which connects to the MRP ring
2nd Ring Port
Chooses the port which connects to the MRP ring
Page 26
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
25
4.4 STP/RSTP/MSTP
4.4.1 STP/RSTP
STP (Spanning Tree Protocol), and its advanced versions RSTP (Rapid Spanning Tree
Protocol) and MSTP (Multiple Spanning Tree Protocol), are designed to prevent network loops
and provide network redundancy. Network loops occur frequently in large networks as when
two or more paths run to the same destination, broadcast packets may get in to an infinite loop
and hence causing congestion in the network. STP can identify the best path to the destination,
and block all other paths. The blocked links will stay connected but inactive. When the best
path fails, the blocked links will be activated. Compared to STP which recovers a link in 30 to
50 seconds, RSTP can shorten the time to 5 to 6 seconds.
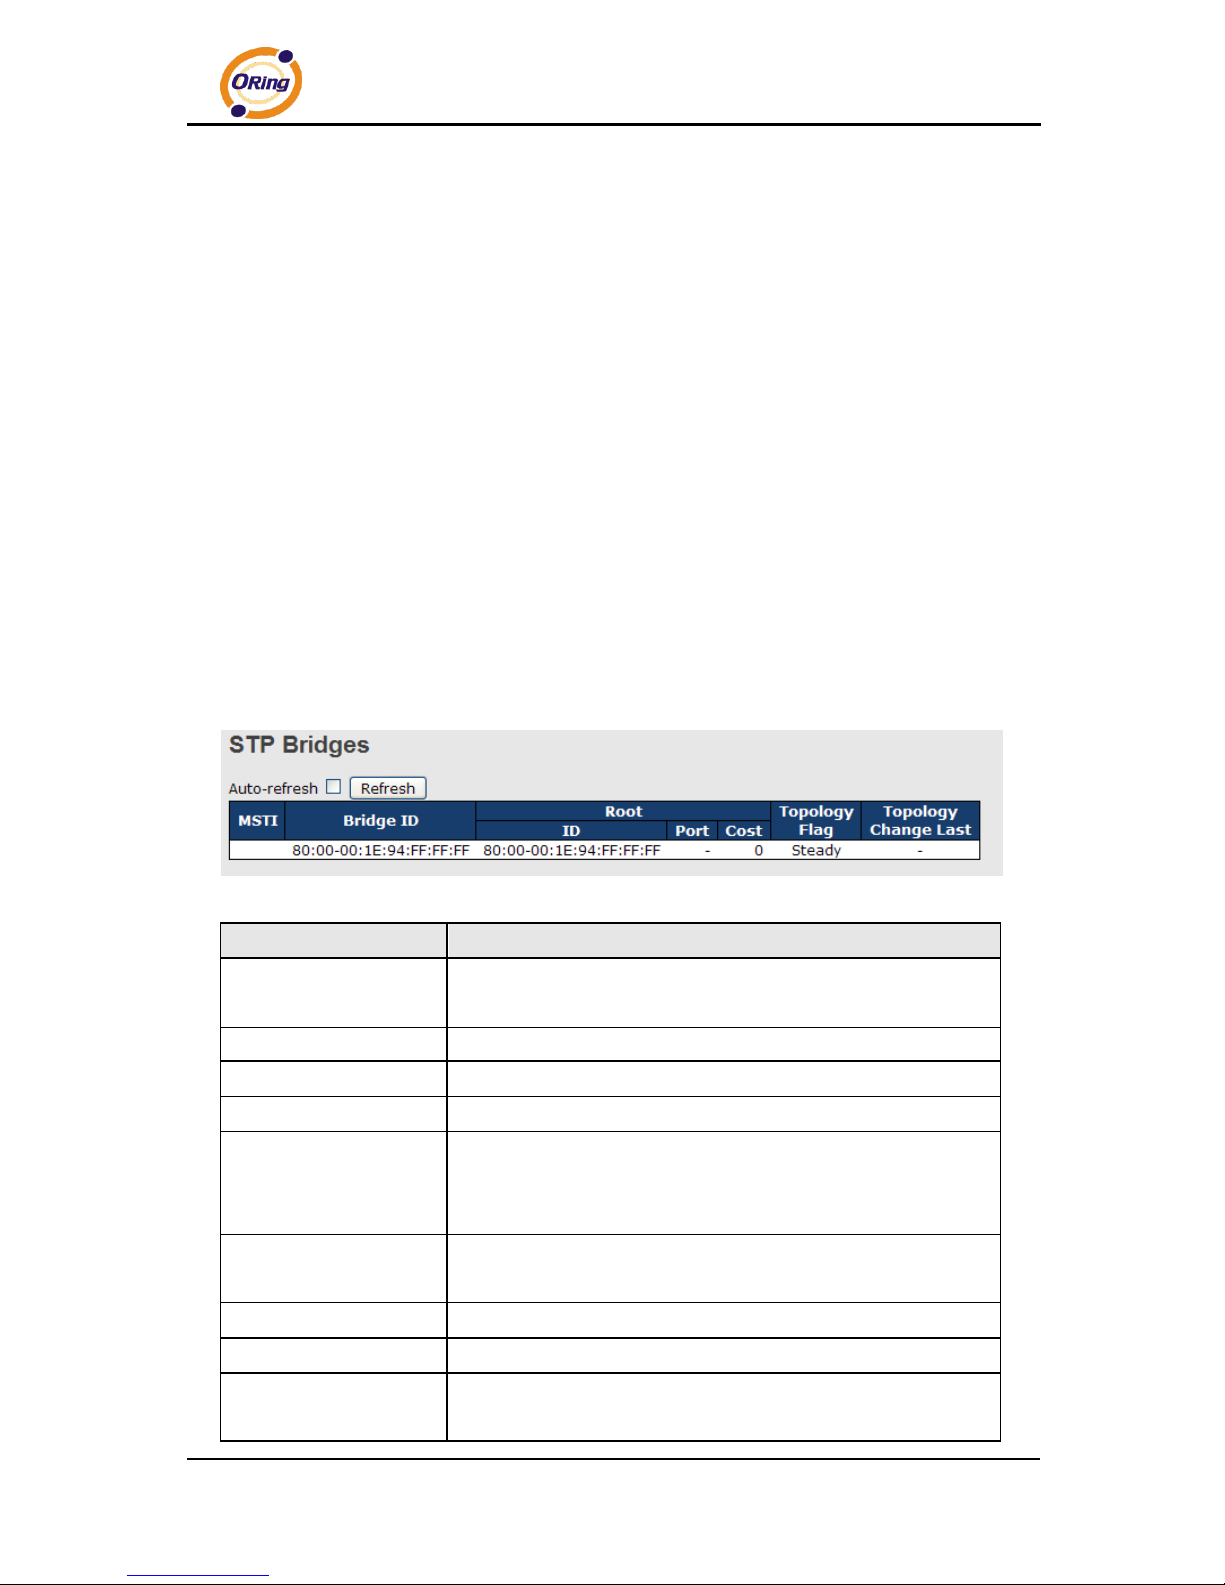
STP Bridge Status
This page shows the status for all STP bridge instance.
Label
Description
MSTI
The bridge instance. You can also link to the STP detailed
bridge status.
Bridge ID
The bridge ID of this bridge instance.
Root ID
The bridge ID of the currently selected root bridge.
Root Port
The switch port currently assigned the root port role.
Root Cost
Root path cost. For a root bridge, this is zero. For other bridges,
it is the sum of port path costs on the least cost path to the Root
Bridge.
Topology Flag
The current state of the Topology Change Flag for the bridge
instance.
Topology Change Last
The time since last Topology Change occurred.
Refresh
Click to refresh the page immediately.
Auto-refresh
Check this box to enable an automatic refresh of the page at
regular intervals.
Page 27
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
26
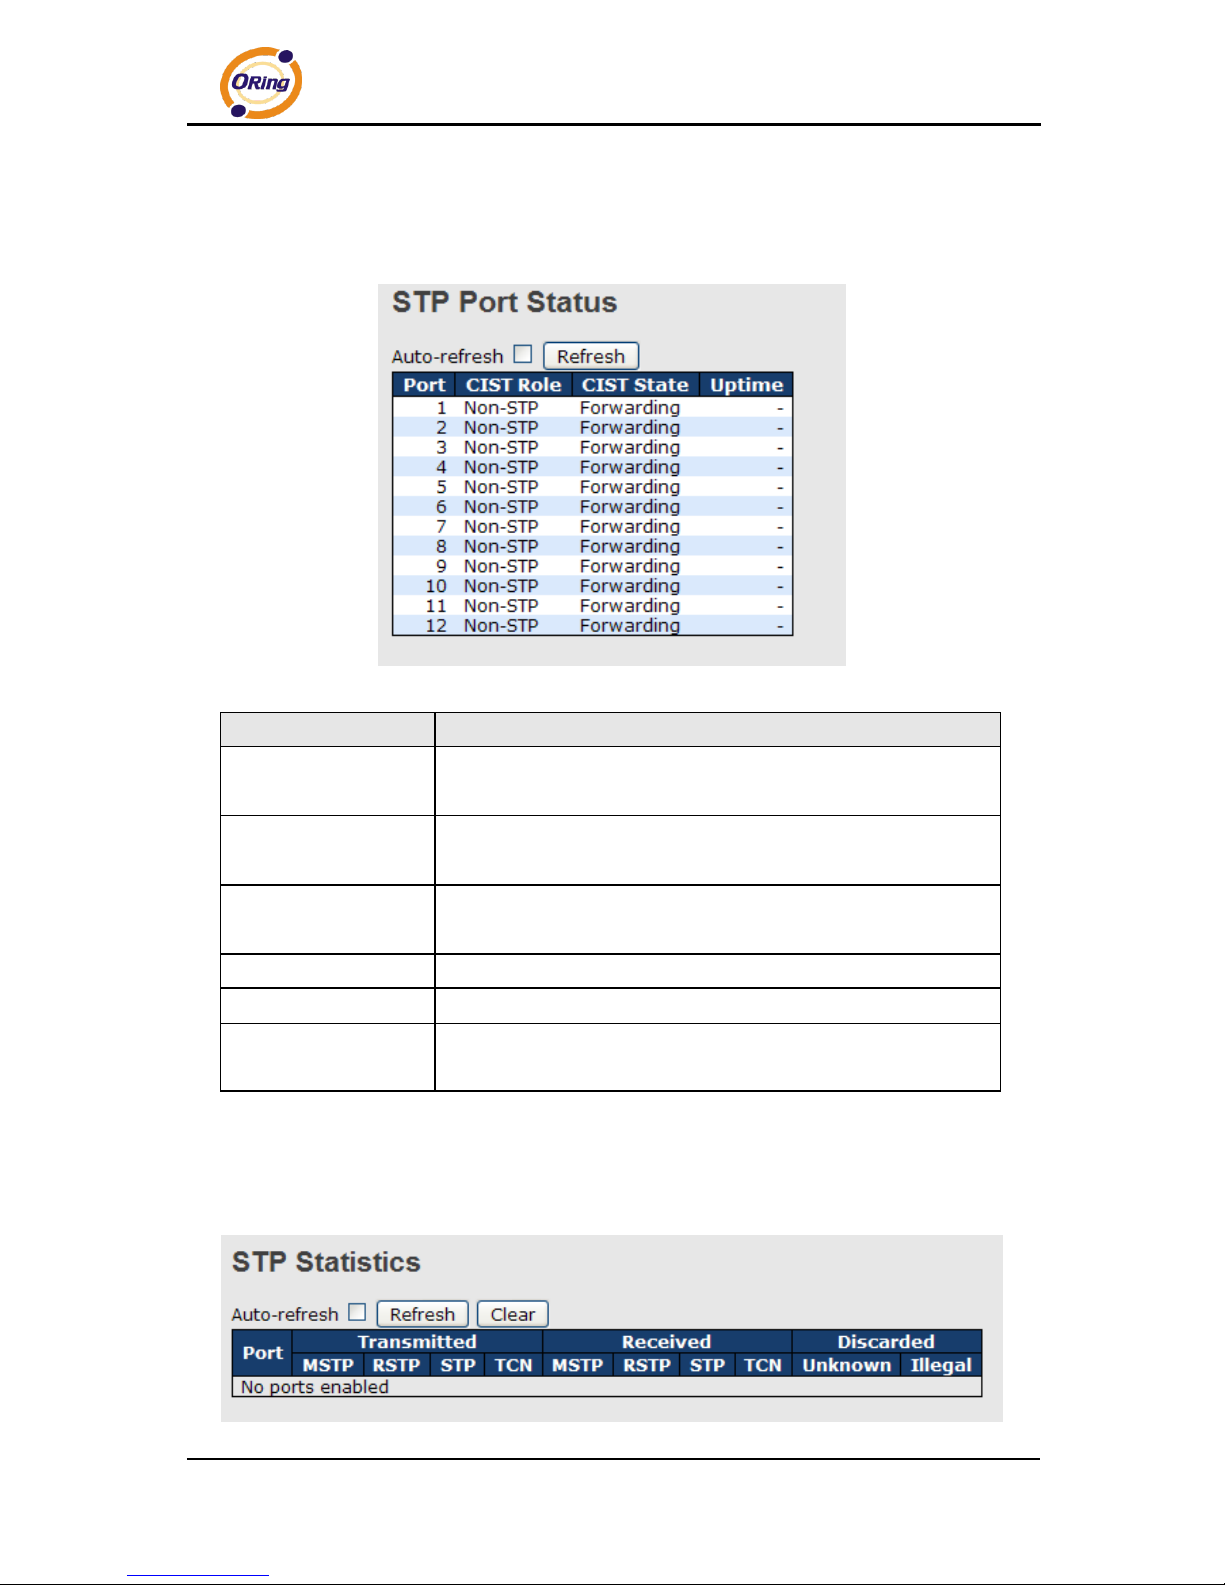
STP Port Status
This page displays the STP port status for the currently selected switch.
Label
Description
Port
The switch port number to which the following settings will be
applied.
CIST Role
The current STP port role of the CIST port. The values include:
AlternatePort, BackupPort, RootPort, and DesignatedPort.
State
The current STP port state of the CIST port. The values include:
Blocking, Learning, and Forwarding.
Uptime
The time since the bridge port is last initialized
Refresh
Click to refresh the page immediately.
Auto-refresh
Check this box to enable an automatic refresh of the page at
regular intervals.
STP Statistics
This page displays the STP port statistics for the currently selected switch.
Page 28
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
27
Label
Description
Port
The switch port number to which the following settings will be
applied.
RSTP
The number of RSTP configuration BPDUs received/transmitted
on the port
STP
The number of legacy STP configuration BPDUs
received/transmitted on the port
TCN
The number of (legacy) topology change notification BPDUs
received/transmitted on the port
Discarded Unknown
The number of unknown spanning tree BPDUs received (and
discarded) on the port.
Discarded Illegal
The number of illegal spanning tree BPDUs received (and
discarded) on the port.
Refresh
Click to refresh the page immediately
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
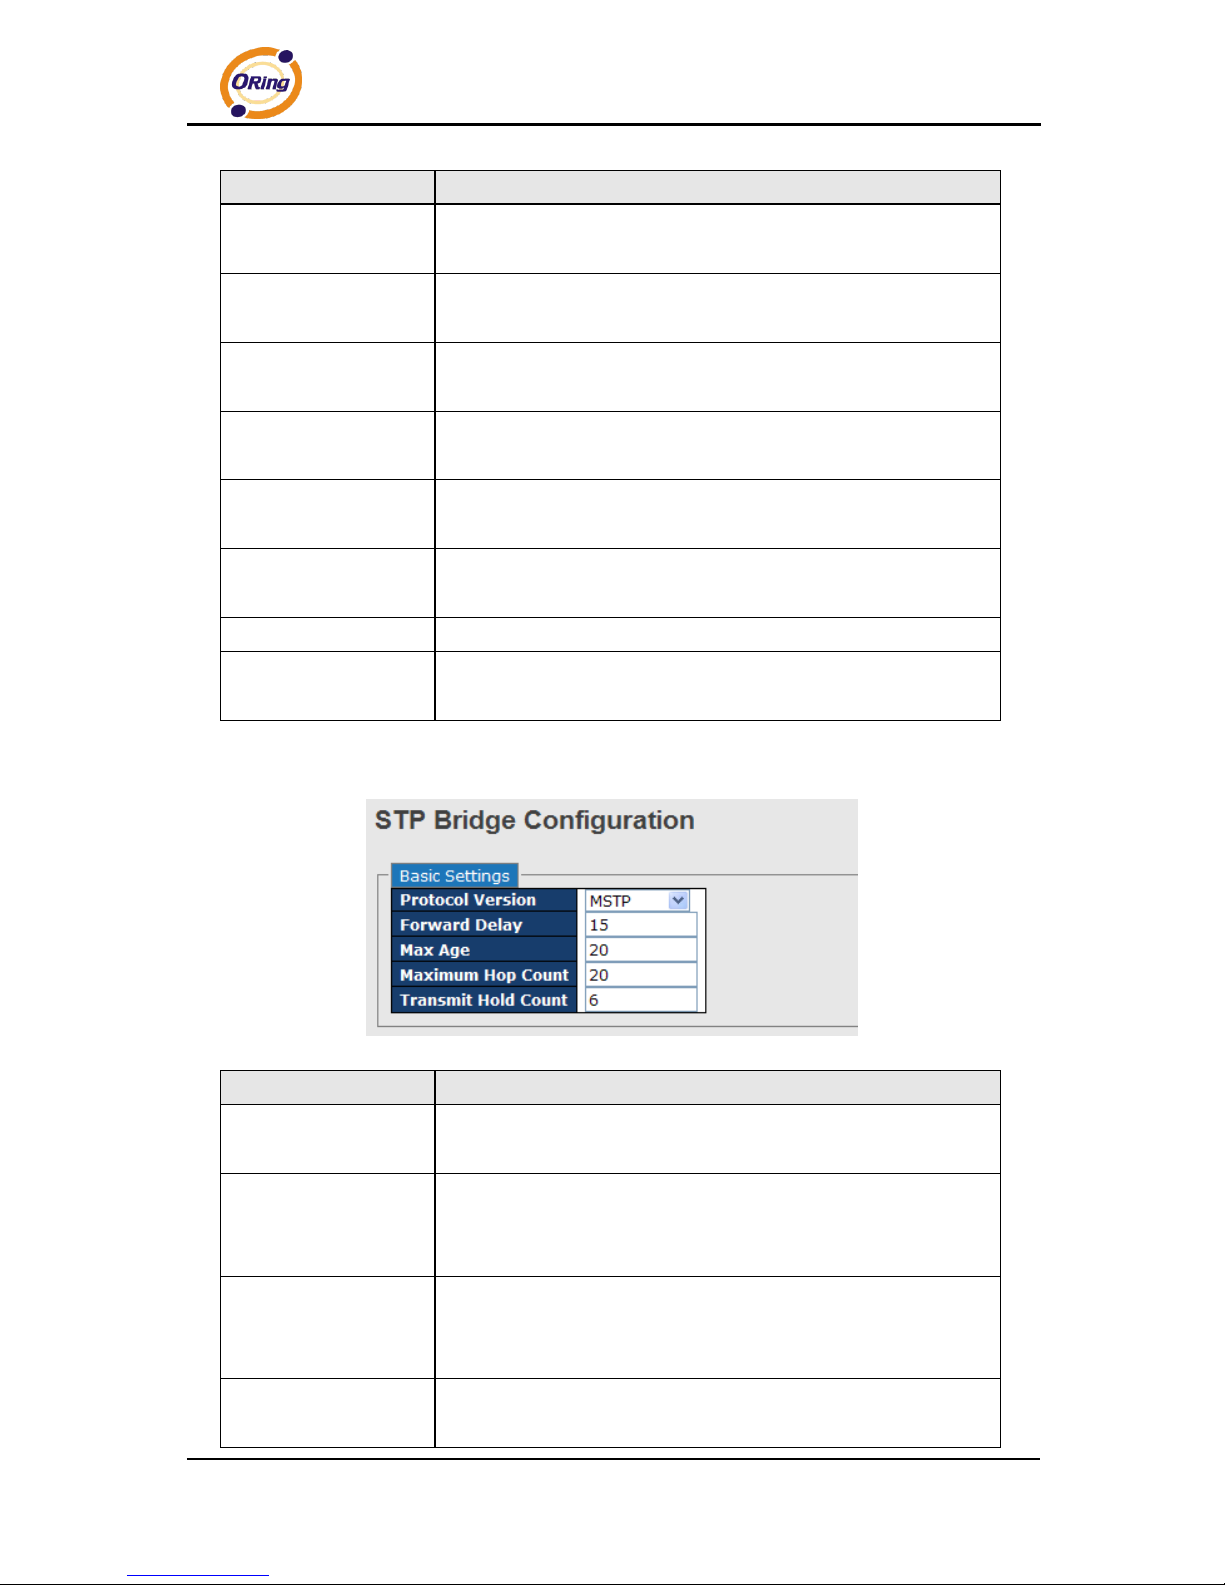
STP Bridge Configurations
Label
Description
Protocol Version
The version of the STP protocol. Valid values include STP, RSTP
and MSTP.
Forward Delay
The delay used by STP bridges to transit root and designated
ports to forwarding (used in STP compatible mode). The range of
valid values is 4 to 30 seconds.
Max Age
The maximum time the information transmitted by the root bridge
is considered valid. The range of valid values is 6 to 40 seconds,
and Max Age must be <= (FwdDelay-1)*2.
Maximum Hop Count
This defines the initial value of remaining hops for MSTI
information generated at the boundary of an MSTI region. It
Page 29
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
28
defines how many bridges a root bridge can distribute its BPDU
information to . The range of valid values is 4 to 30 seconds, and
MaxAge must be <= (FwdDelay-1)*2.
Transmit Hold Count
The number of BPDUs a bridge port can send per second. When
exceeded, transmission of the next BPDU will be delayed. The
range of valid values is 1 to 10 BPDUs per second.
Save
Click to save changes.
Reset
Click to undo any changes made locally and revert to previously
saved values.
4.4.2 MSTP
Since the recovery time of STP and RSTP takes seconds, which are unacceptable in some
industrial applications, MSTP was developed. The technology supports multiple spanning
trees within a network by grouping and mapping multiple VLANs into different spanning-tree
instances, known as MSTIs, to form individual MST regions. Each switch is assigned to an
MST region. Hence, each MST region consists of one or more MSTP switches with the same
VLANs, at least one MST instance, and the same MST region name. Therefore, switches can
use different paths in the network to effectively balance loads.
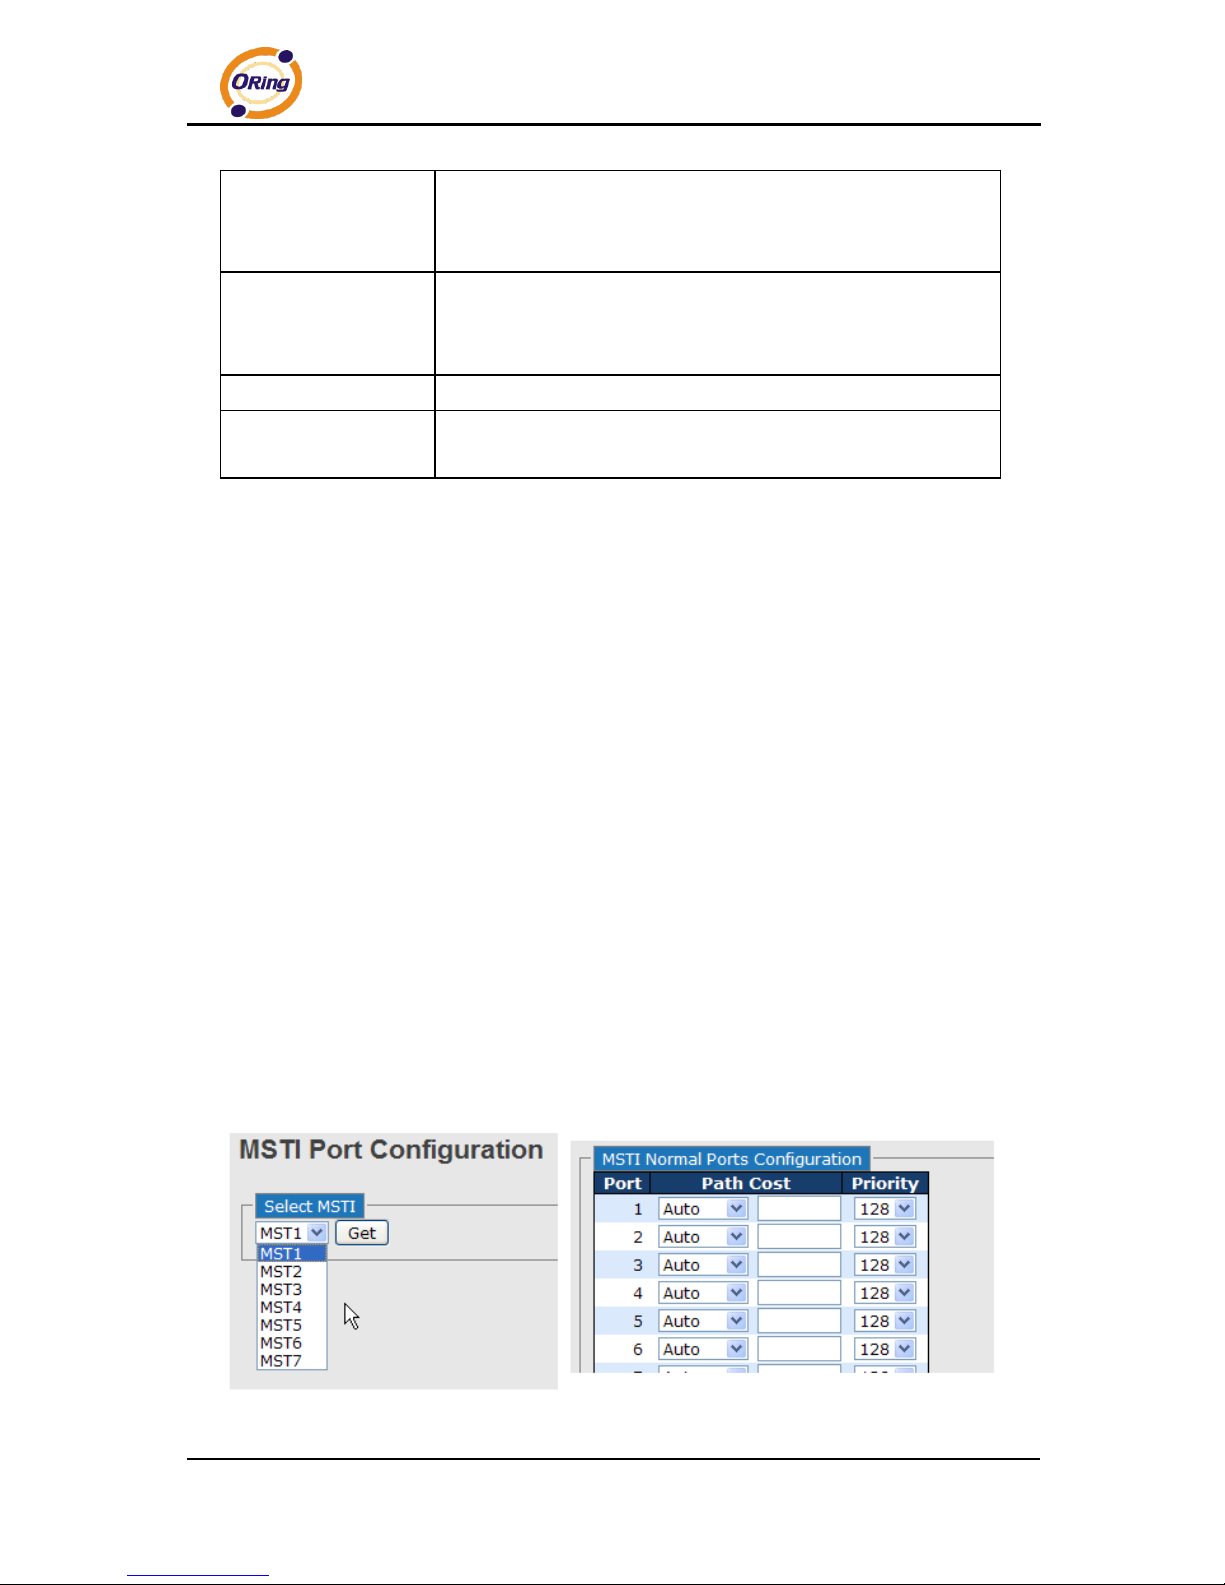
Port Settings
This page allows you to examine and change the configurations of current MSTI ports. A MSTI
port is a virtual port, which is instantiated separately for each active CIST (physical) port for
each MSTI instance configured and applicable for the port. The MSTI instance must be
selected before MSTI port configuration options are displayed.
This page contains MSTI port settings for physical and aggregated ports. The aggregation
settings are stack global.
Page 30
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
29
Label
Description
Port
The switch port number of the corresponding STP CIST (and MSTI) port
Path Cost
Configures the path cost incurred by the port. Auto will set the path cost
according to the physical link speed by using the 802.1D-recommended
values. Specific allows you to enter a user-defined value. The path cost is
used when establishing an active topology for the network. Lower path cost
ports are chosen as forwarding ports in favor of higher path cost ports. The
range of valid values is 1 to 200000000.
Priority
Configures the priority for ports having identical port costs. (See above).
Save
Click to save changes.
Reset
Click to undo any changes made locally and revert to previously saved
values.
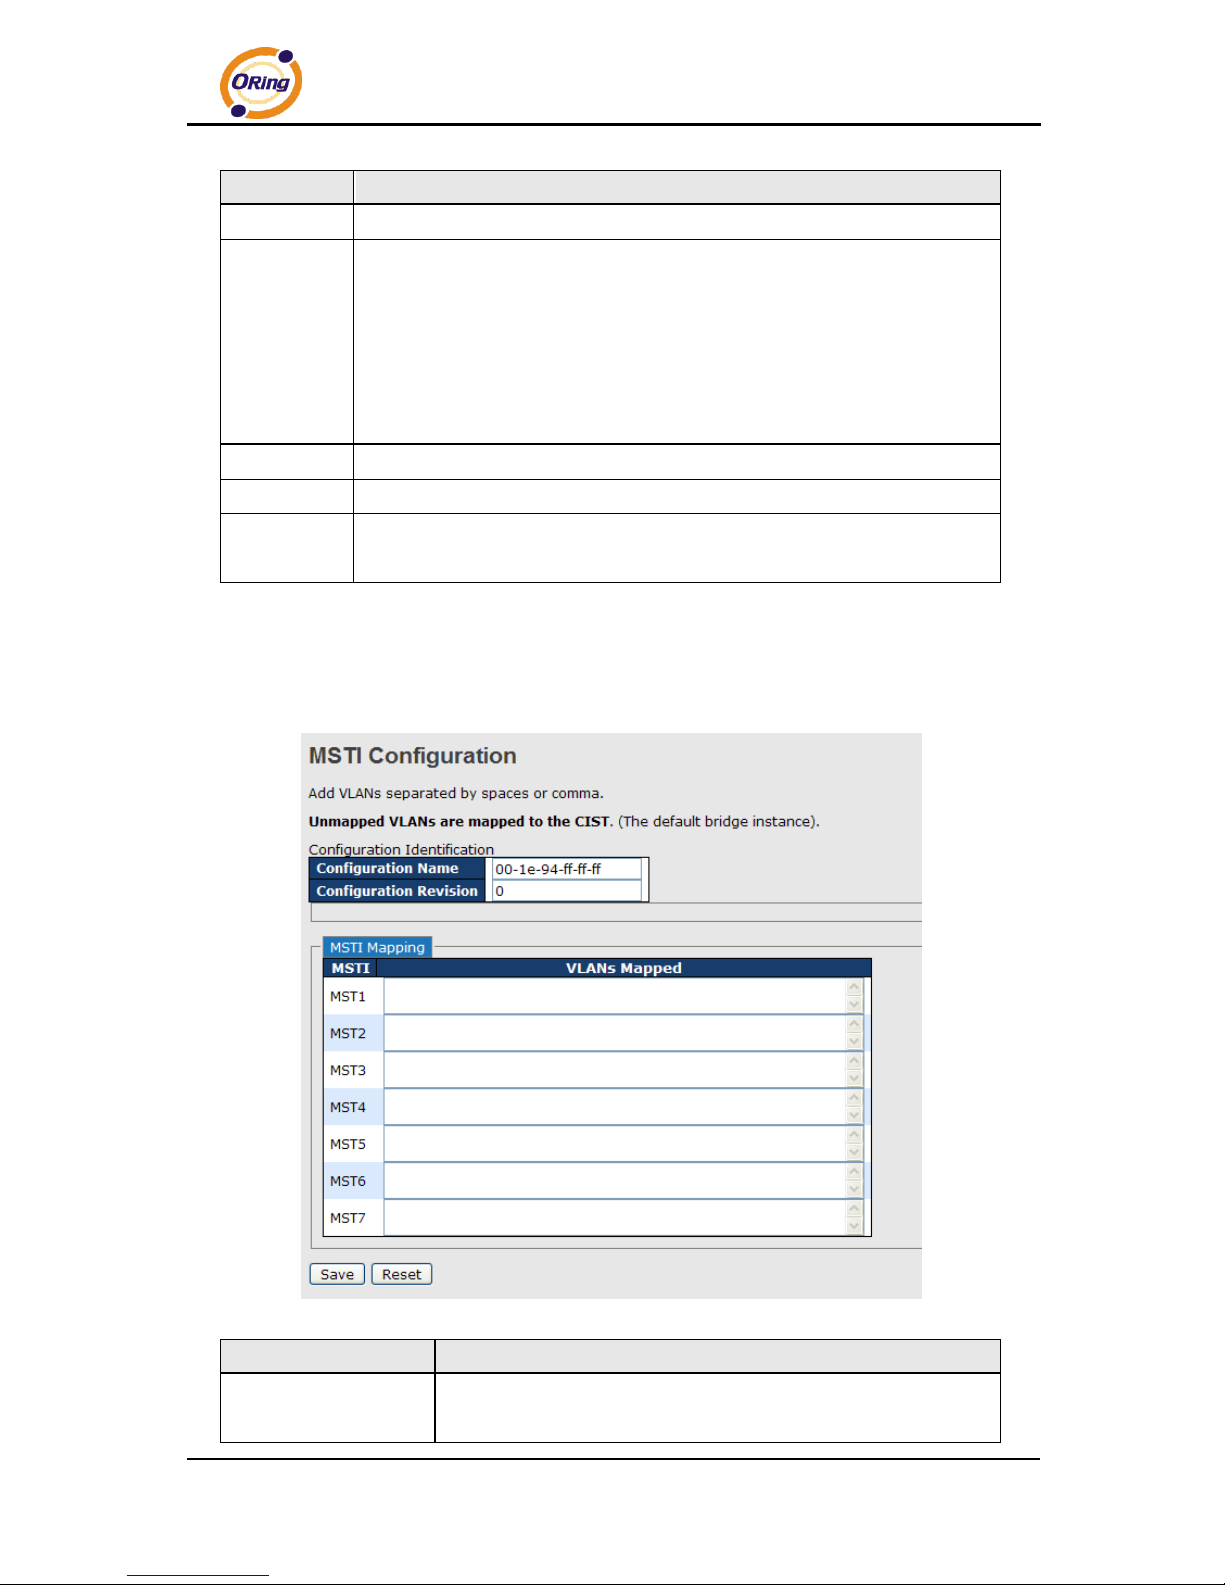
Mapping
This page allows you to examine and change the configurations of current STP MSTI bridge
instance.
Label
Description
Configuration Name
The name which identifies the VLAN to MSTI mapping. Bridges
must share the name and revision (see below), as well as the
Page 31
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
30
VLAN-to-MSTI mapping configurations in order to share spanning
trees for MSTIs (intra-region). The name should not exceed 32
characters.
Configuration
Revision
Revision of the MSTI configuration named above. This must be
an integer between 0 and 65535.
MSTI
The bridge instance. The CIST is not available for explicit
mapping, as it will receive the VLANs not explicitly mapped.
VLANS Mapped
The list of VLANs mapped to the MSTI. The VLANs must be
separated with commas and/or space. A VLAN can only be
mapped to one MSTI. An unused MSTI will be left empty (ex.
without any mapped VLANs).
Save
Click to save changes.
Reset
Click to undo any changes made locally and revert to previously
saved values.
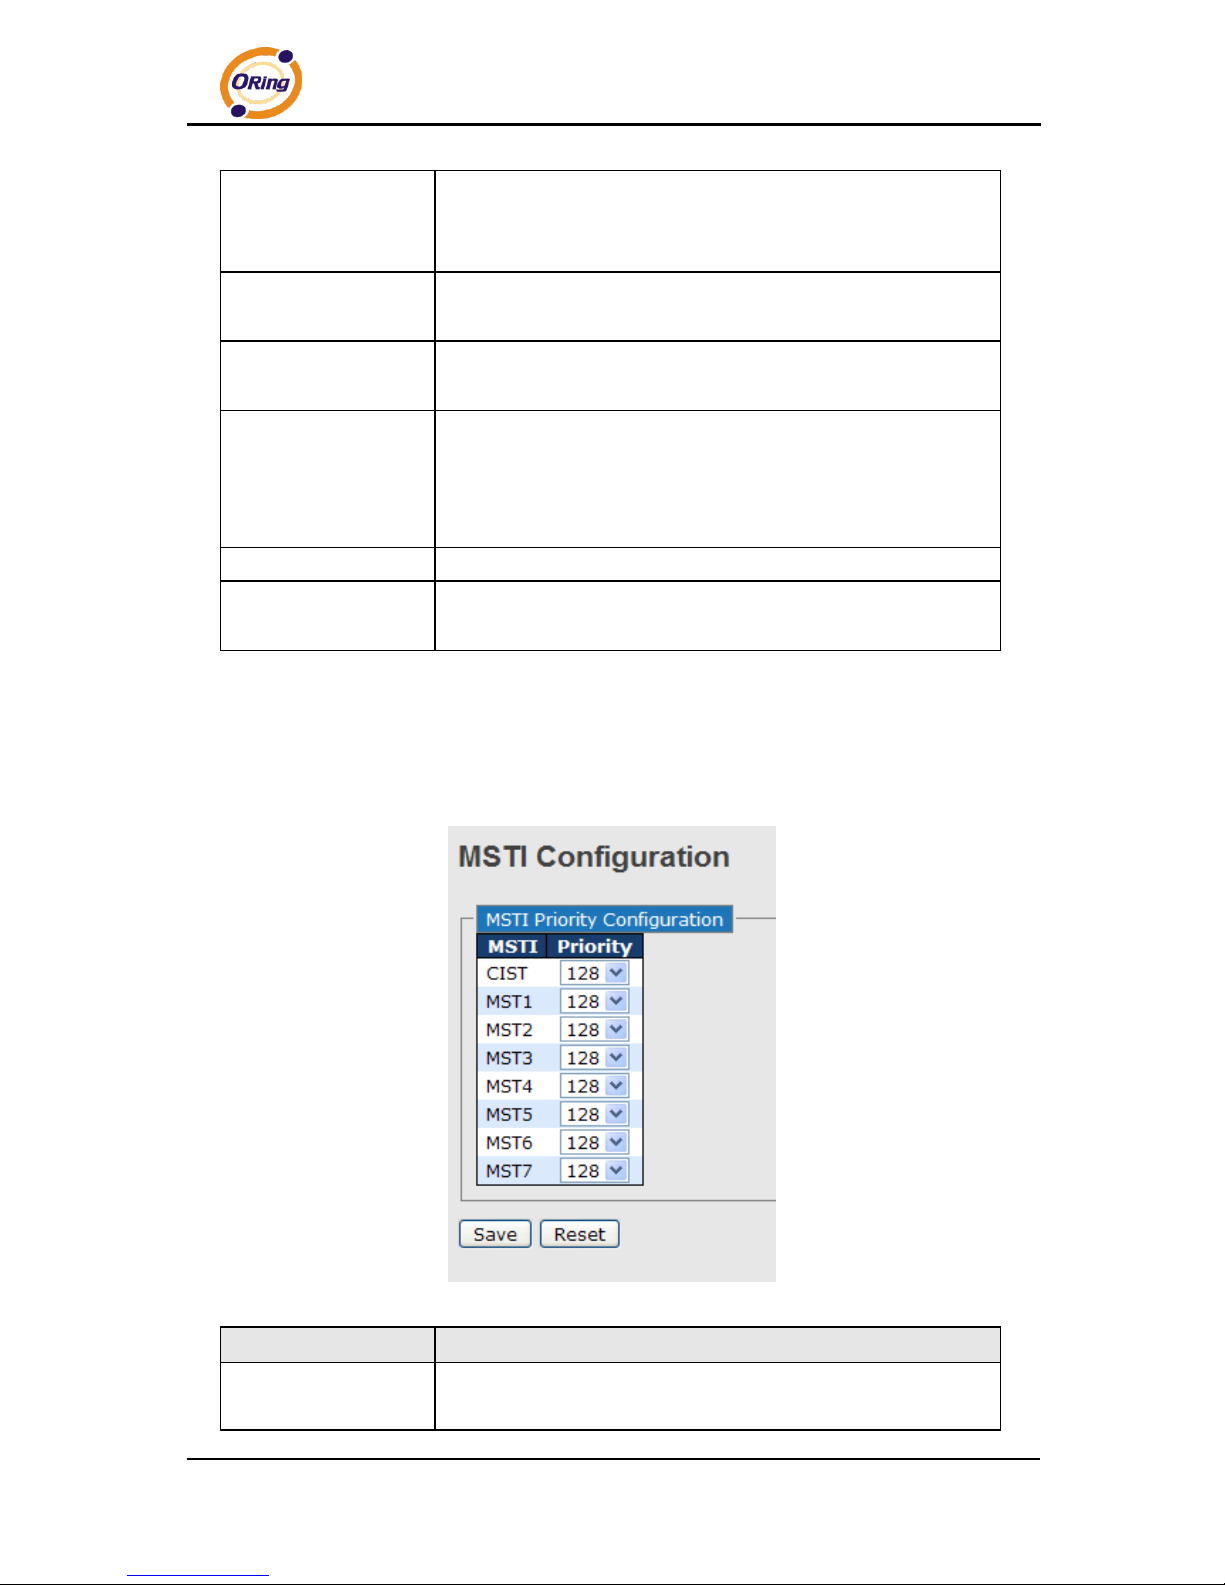
Priority
This page allows you to examine and change the configurations of current STP MSTI bridge
instance priority.
Label
Description
MSTI
The bridge instance. CIST is the default instance, which is always
active.
Page 32
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
31
Priority
Indicates bridge priority. The lower the value, the higher the
priority. The bridge priority, MSTI instance number, and the 6-byte
MAC address of the switch forms a bridge identifier.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
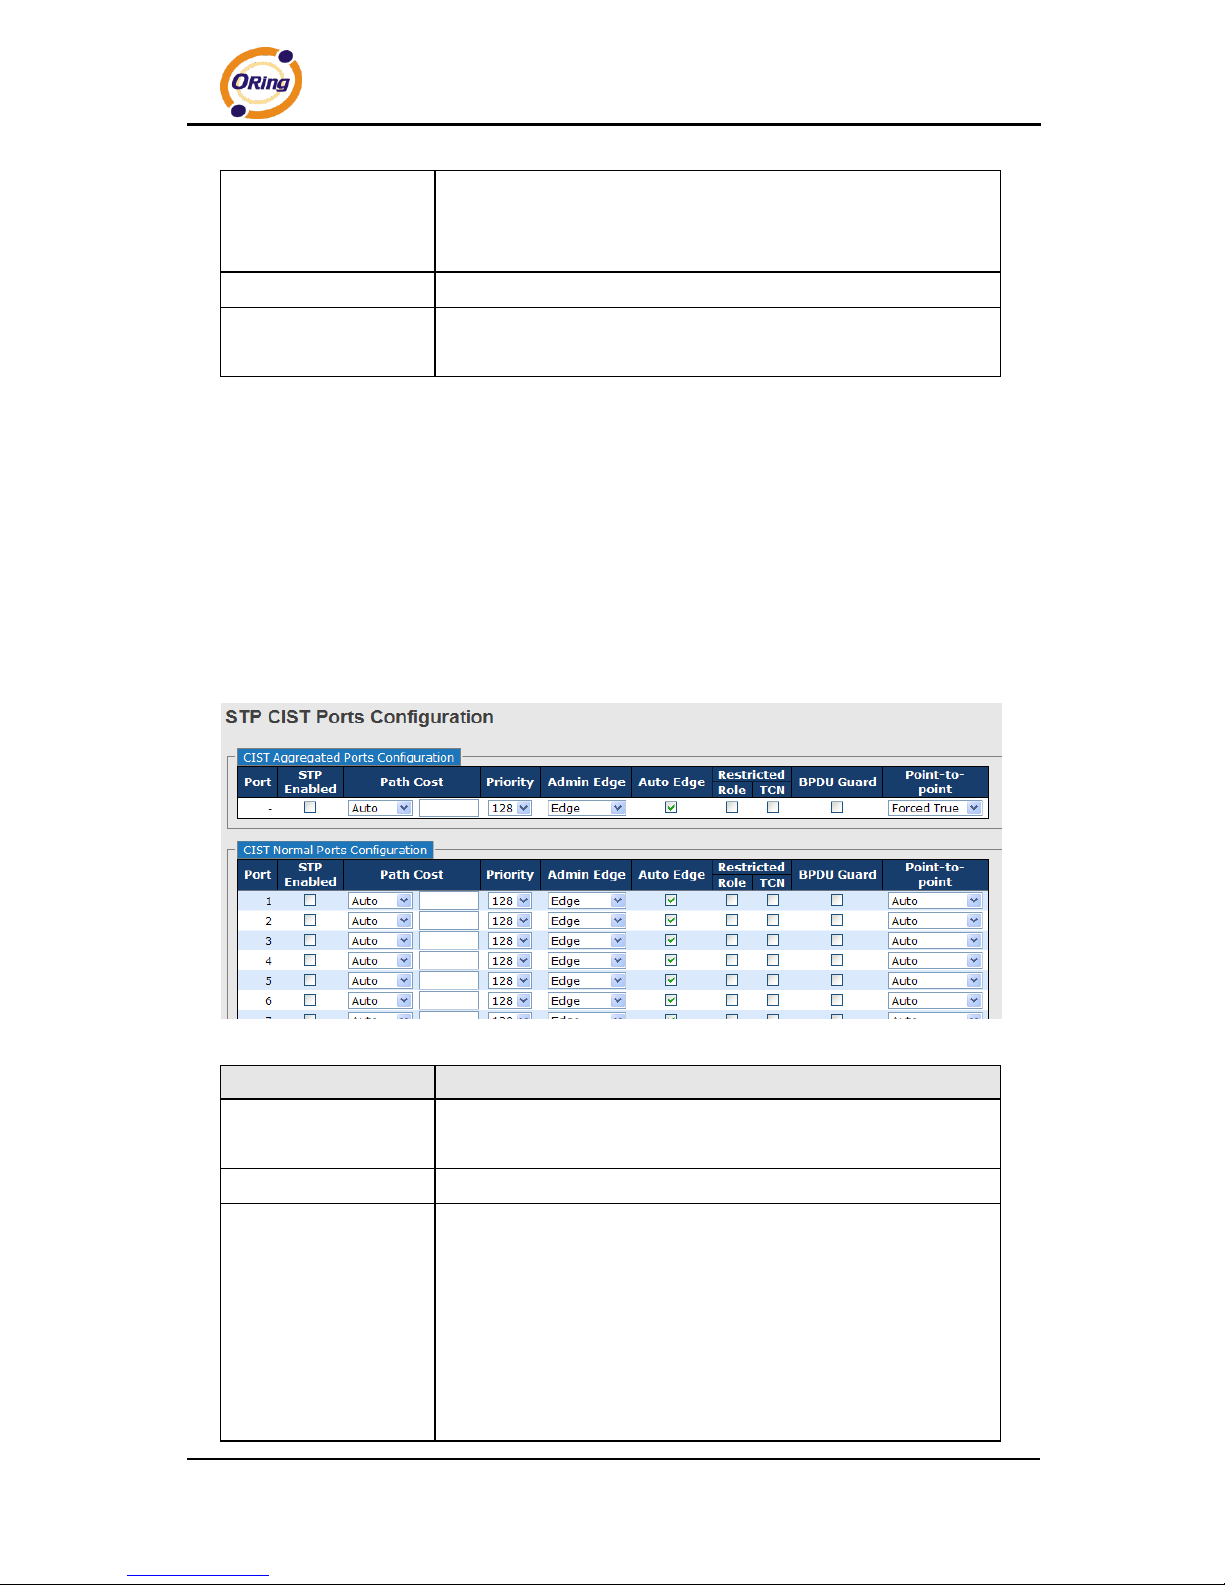
4.4.3 CIST
With the ability to cross regional boundaries, CIST is used by MSTP to communicate with other
MSTP regions and with any RSTP and STP single-instance spanning trees in the network. Any
boundary port, that is, if it is connected to another region, will automatically belongs solely to
CIST, even if it is assigned to an MSTI. All VLANs that are not members of particular MSTIs
are members of the CIST.
Port Settings
Label
Description
Port
The switch port number to which the following settings will be
applied.
STP Enabled
Check to enable STP for the port
Path Cost
Configures the path cost incurred by the port. Auto will set the
path cost according to the physical link speed by using the
802.1D-recommended values. Specific allows you to enter a
user-defined value. The path cost is used when establishing an
active topology for the network. Lower path cost ports are chosen
as forwarding ports in favor of higher path cost ports. The range of
valid values is 1 to 200000000.
Page 33
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
32
Priority
Configures the priority for ports having identical port costs. (See
above).
OpenEdge (setate
flag)
A flag indicating whether the port is connected directly to edge
devices or not (no bridges attached). Transiting to the forwarding
state is faster for edge ports (operEdge set to true) than other
ports.
AdminEdge
Configures the operEdge flag to start as set or cleared.(the initial
operEdge state when a port is initialized).
AutoEdge
Check to enable the bridge to detect edges at the bridge port
automatically. This allows operEdge to be derived from whether
BPDUs are received on the port or not.
Restricted Role
When enabled, the port will not be selected as root port for CIST
or any MSTI, even if it has the best spanning tree priority vector.
Such a port will be selected as an alternate port after the root port
has been selected. If set, spanning trees will lose connectivity. It
can be set by a network administrator to prevent bridges outside a
core region of the network from influencing the active spanning
tree topology because those bridges are not under the full control
of the administrator. This feature is also known as Root Guard.
Restricted TCN
When enabled, the port will not propagate received topology
change notifications and topology changes to other ports. If set, it
will cause temporary disconnection after changes in an active
spanning trees topology as a result of persistent incorrectly
learned station location information. It is set by a network
administrator to prevent bridges outside a core region of the
network from causing address flushing in that region because
those bridges are not under the full control of the administrator or
is the physical link state for the attached LANs transitions
frequently.
Point2Point
Configures whether the port connects to a point-to-point LAN
rather than a shared medium. This can be configured
automatically or set to true or false manually. Transiting to
forwarding state is faster for point-to-point LANs than for shared
media.
Save
Click to save changes.
Reset
Click to undo any changes made locally and revert to previously
saved values.
Page 34
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
33
4.5 Fast Recovery
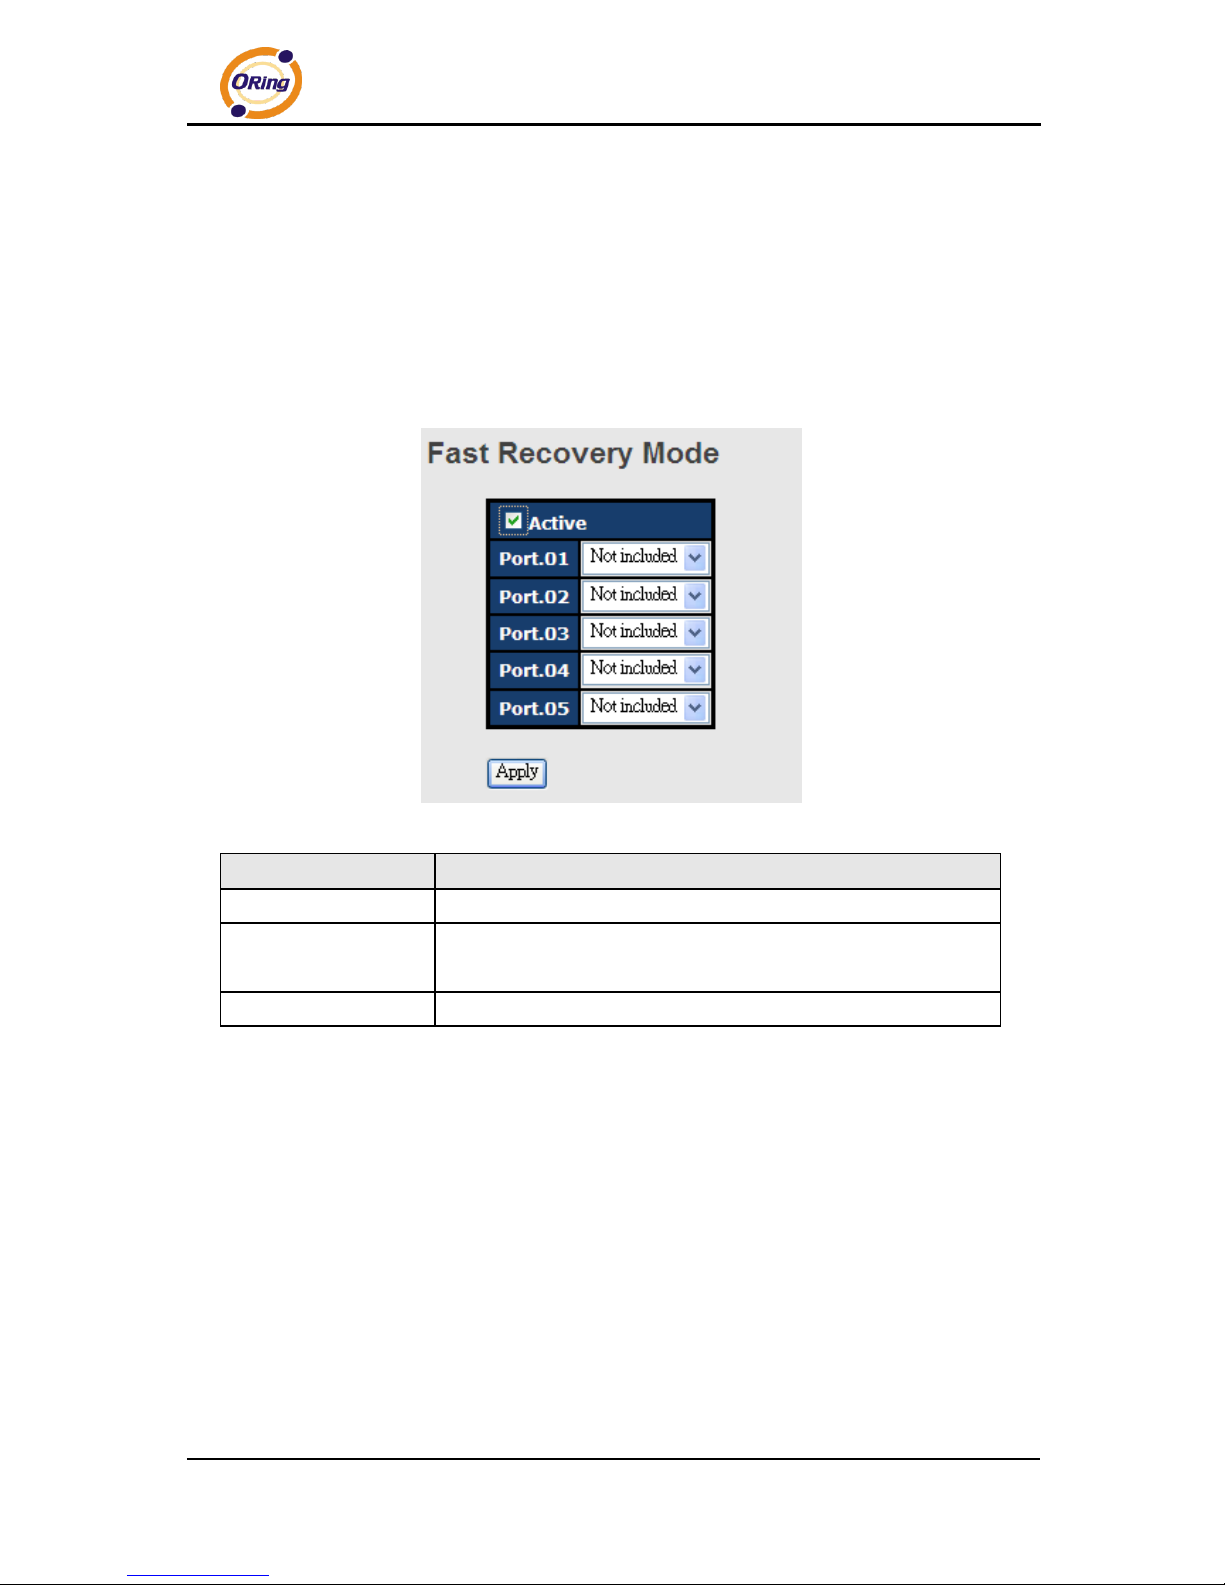
Fast recovery mode can be set to connect multiple ports to one or more switches. The
IGS-9844/9848GPF with fast recovery mode will provide redundant links. Fast recovery mode
supports 12 priorities. Only the first priority will be the active port, and the other ports with
different priorities will be backup ports.
Label
Description
Active
Activate fast recovery mode
port
Ports can be set to 12 priorities. Only the port with the highest
priority will be the active port. 1st Priority is the highest.
Apply
Click to activate the configurations.
Page 35
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
34
Management
The switch can be controlled via a built-in web server which supports Internet Explorer
(Internet Explorer 5.0 or above versions) and other Web browsers such as Chrome. Therefore,
you can manage and configure the switch easily and remotely. You can also upgrade firmware
via a Web browser. The Web management function not only reduces network bandwidth
consumption, but also enhances access speed and provides a user-friendly viewing screen.
Note: By default, IE5.0 or later version do not allow Java applets to open sockets. You need to modify the browser
setting separately in order to enable Java applets for network ports.
Management via Web Browser
Follow the steps below to manage your switch via a Web browser
System Login
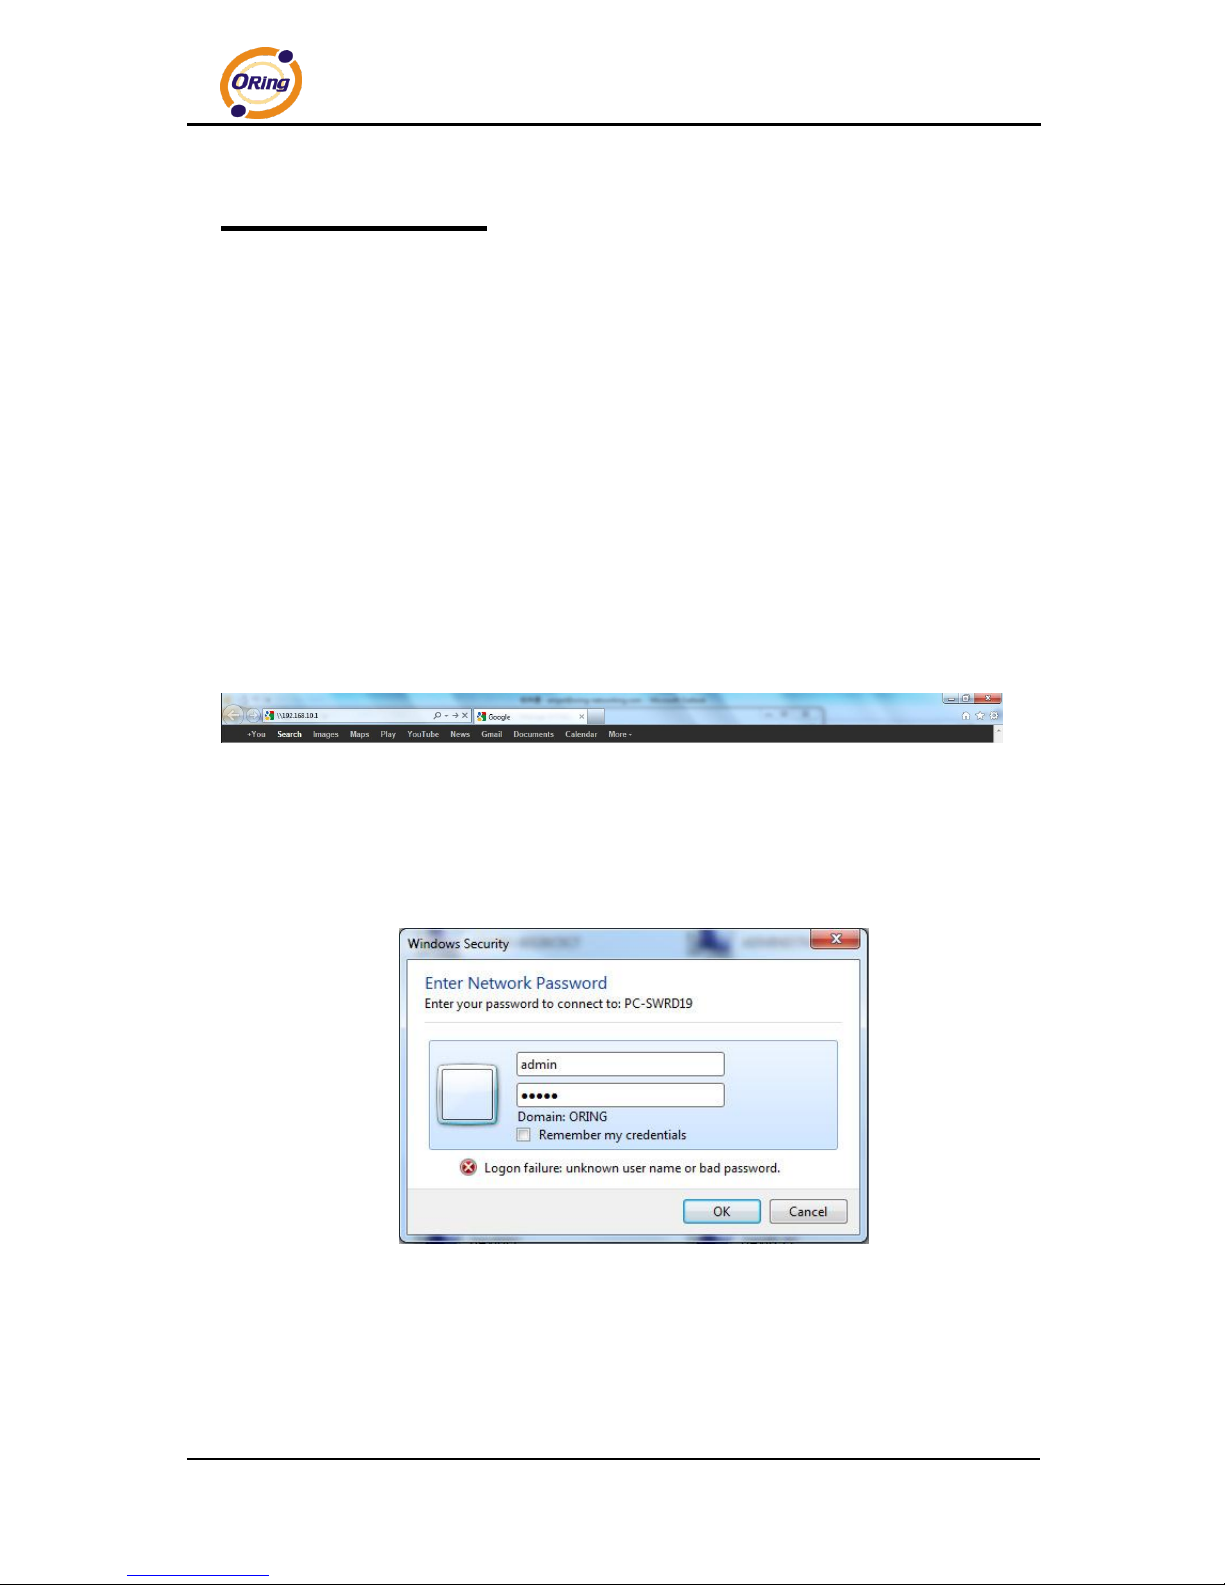
1. Launch an Internet Explorer.
2. Type http:// and the IP address of the switch. Press Enter.
3. A login screen appears.
4. Type in the username and password. The default username and password is
admin.
5. Press Enter or click OK, the management page appears.
Note: you can use the following default values:
IP Address: 192.168.10.1
Subnet Mask: 255.255.255.0
Default Gateway: 192.168.10.254
Page 36
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
35
User Name: admin
Password: admin
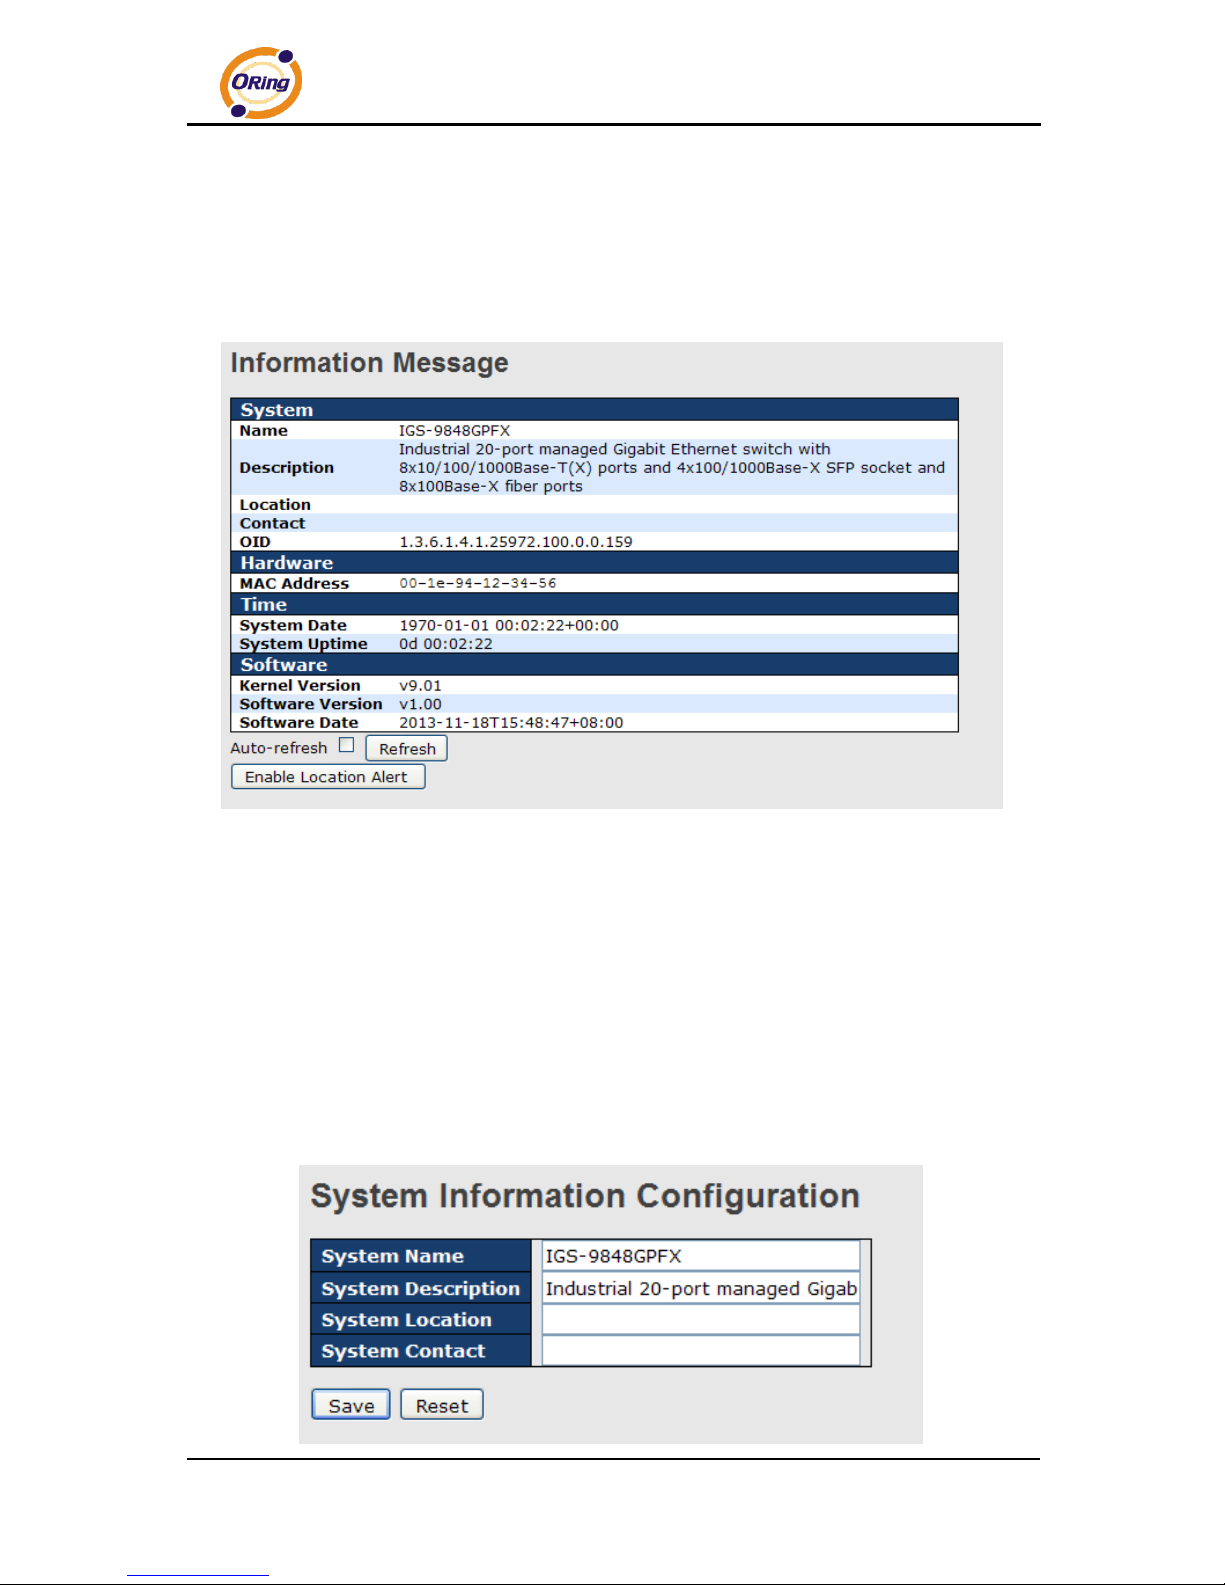
After logging in, you will see the information of the switch as below.
On the right hand side of the management interface shows links to various settings. Clicking
on the links will bring you to individual configuration pages.
5.1 Basic Settings
The Basic Settings page allows you to configure the basic functions of the switch.
5.1.1 System Information
This page shows the general information of the switch.
Page 37
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
36
Label
Description
System Name
An administratively assigned name for the managed node. By
convention, this is the node's fully-qualified domain name. A
domain name is a text string consisting of alphabets (A-Z, a-z),
digits (0-9), and minus sign (-). Space is not allowed to be part of
the name. The first character must be an alpha character. And the
first or last character must not be a minus sign. The allowed string
length is 0 to 255.
System Description
Description of the device
System Location
The physical location of the node (e.g., telephone closet, 3rd
floor). The allowed string length is 0 to 255, and only ASCII
characters from 32 to 126 are allowed.
System Contact
The textual identification of the contact person for this managed
node, together with information on how to contact this person.
The allowed string length is 0 to 255, and only ASCII characters
from 32 to 126 are allowed.
System Timezone
offset(minutes)
Provides the time-zone offset from UTC/GMT.
The offset is given in minutes east of GMT. The valid range is from
-720 to 720 minutes.
Save
Click to save changes.
Reset
Click to undo any changes made locally and revert to previously
saved values.
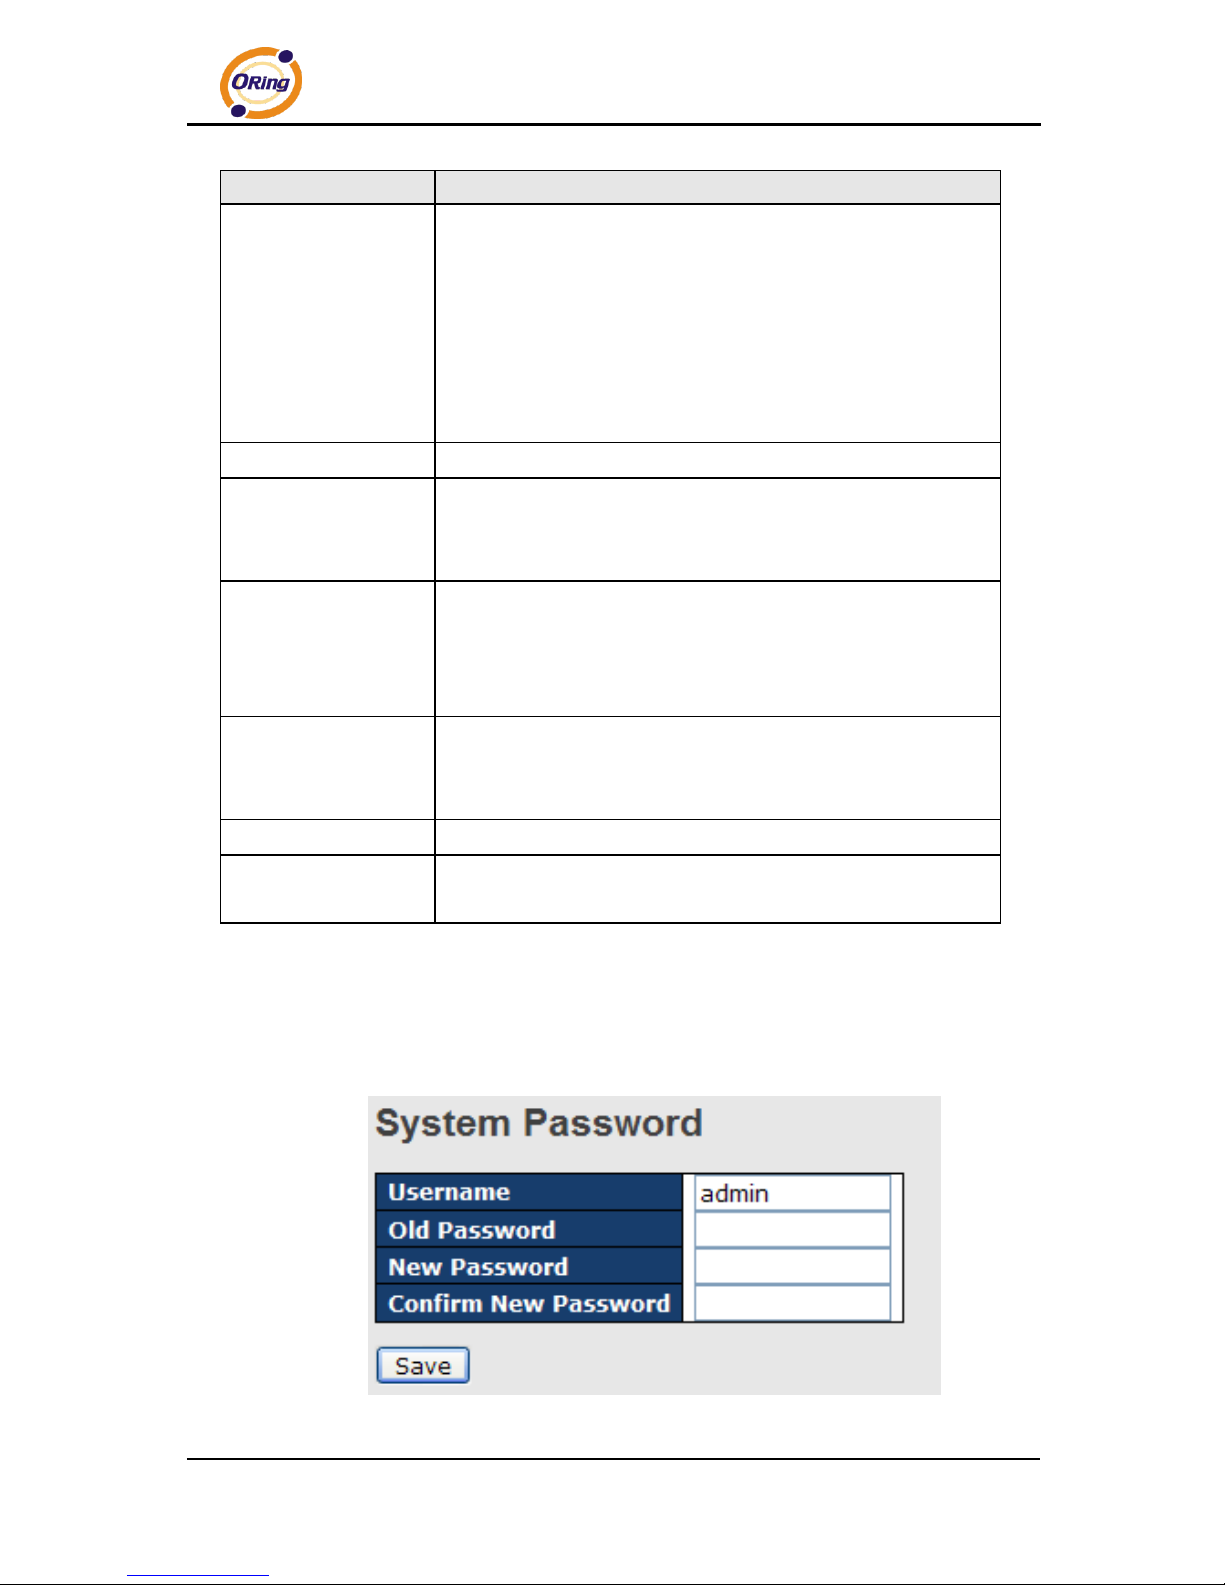
5.1.2 Admin & Password
This page allows you to configure the system password required to access the web pages or
log in from CLI.
Page 38
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
37
Label
Description
Old Password
The existing password. If this is incorrect, you cannot set the new
password.
New Password
The new system password. The allowed string length is 0 to 31,
and only ASCII characters from 32 to 126 are allowed.
Confirm New
Password
Re-type the new password.
Save
Click to save changes.
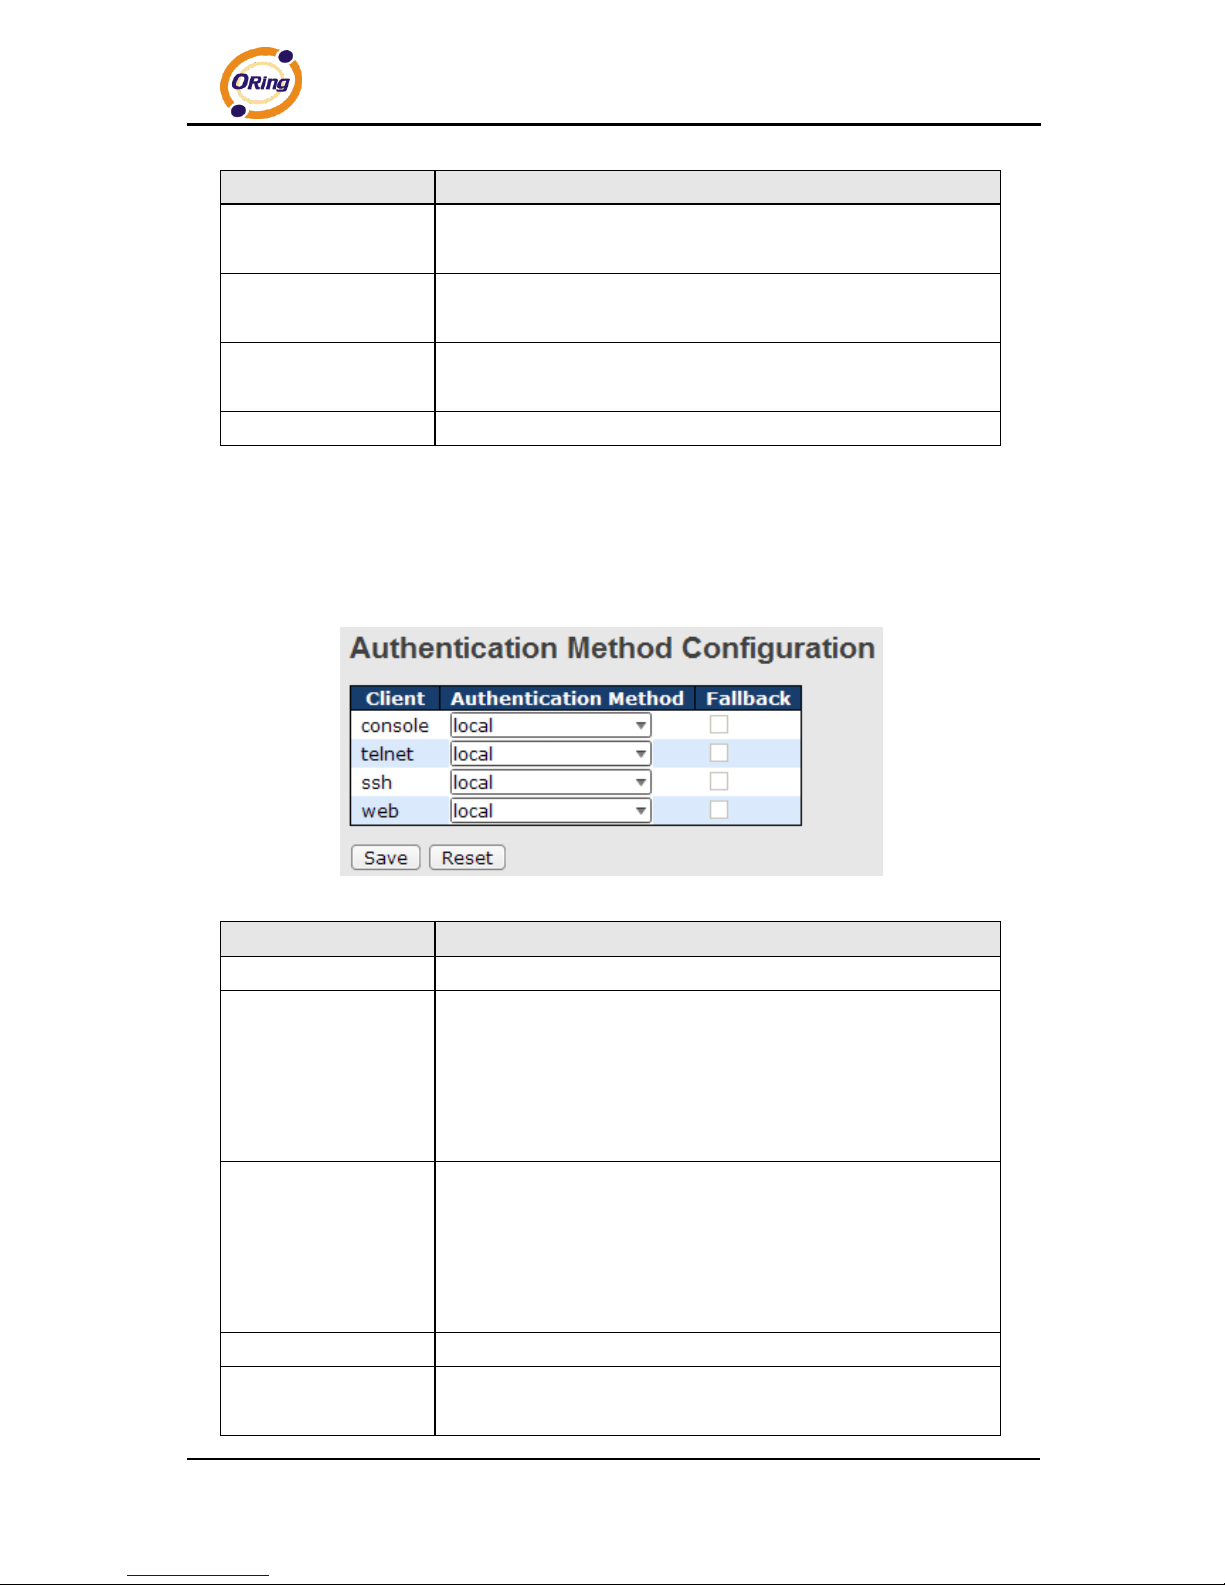
5.1.3 Authentication
This page allows you to configure how a user is authenticated when he/she logs into the switch
via one of the management interfaces.
Label
Description
Client
The management client for which the configuration below applies.
Authentication
Method
Authentication Method can be set to one of the following values:
None: authentication is disabled and login is not possible.
Local: local user database on the switch is used for
authentication.
Radius: a remote RADIUS server is used for authentication.
Fallback
Check to enable fallback to local authentication.
If none of the configured authentication servers are active, the
local user database is used for authentication.
This is only possible if Authentication Method is set to a value
other than none or local.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
Page 39
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
38
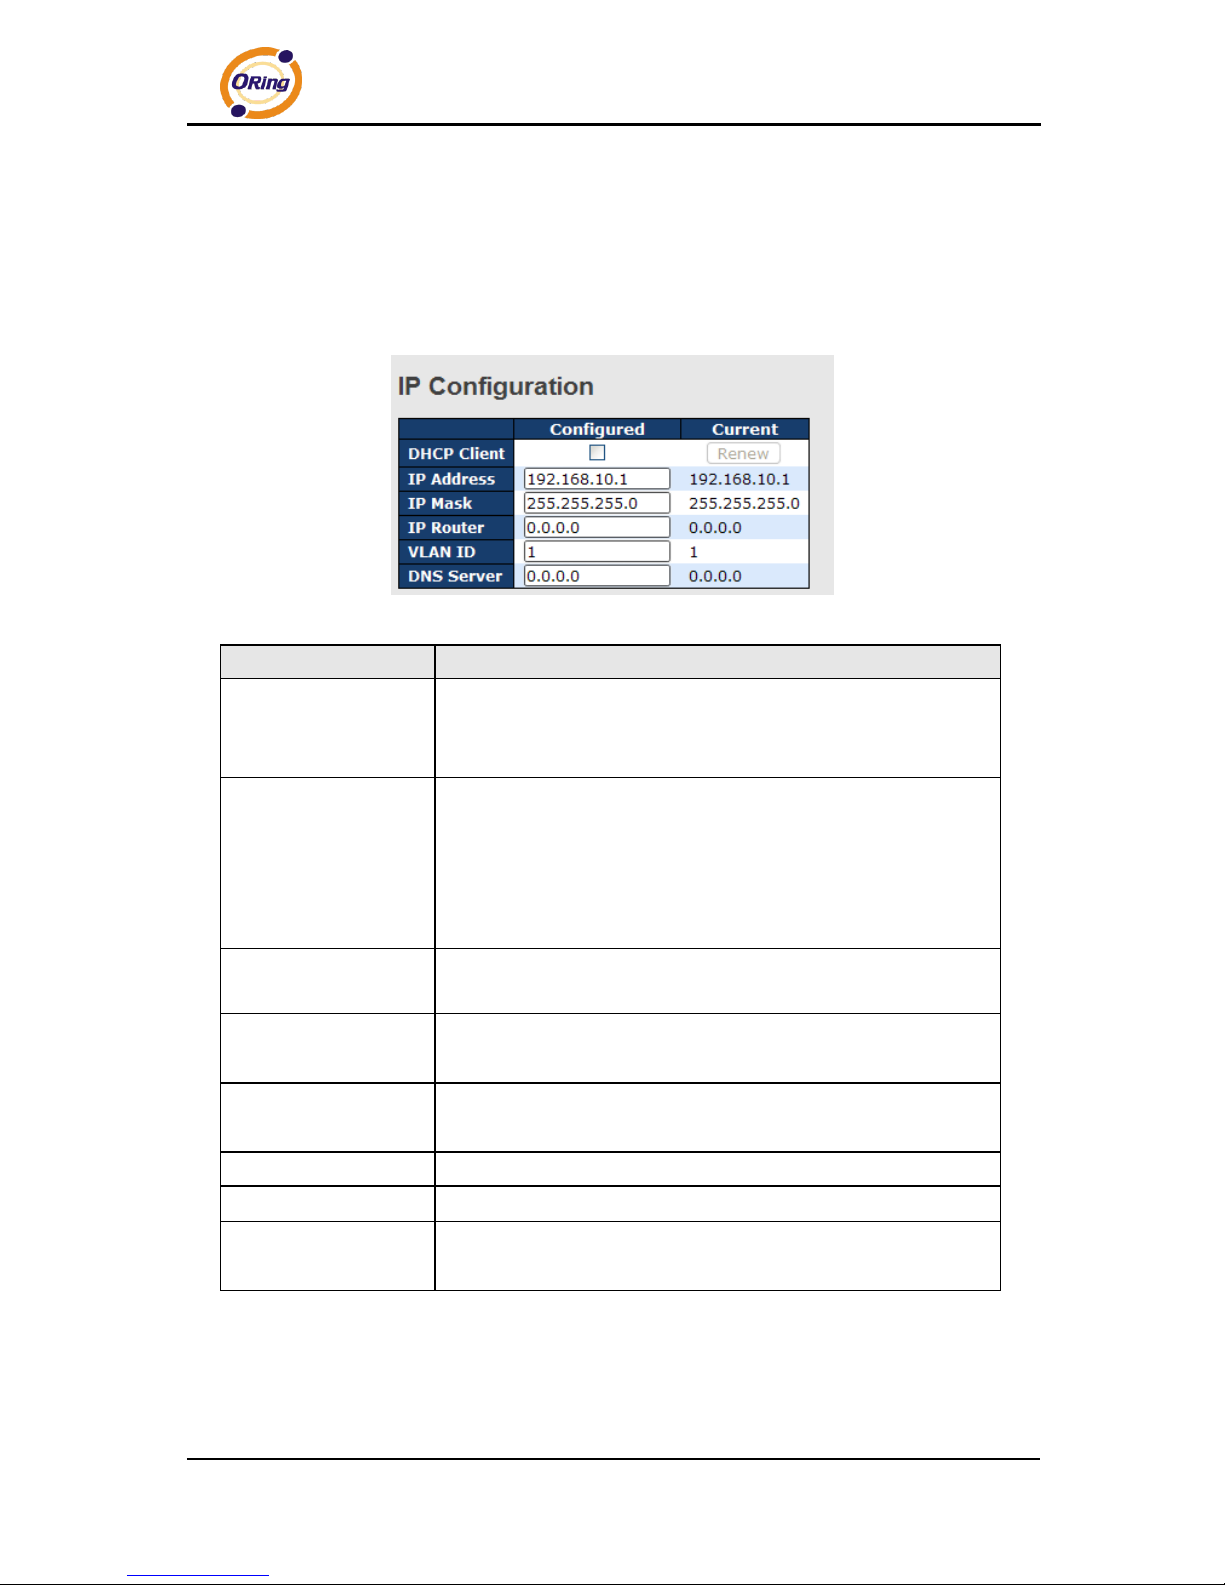
5.1.4 IP Settings
This page allows you to configure IP information for the switch. You can specify configure the
settings manually by disabling DHCP Client. After inputting the values, click Renew and the
new values will be applied, which will be displayed under Current.
Label
Description
DHCP Client
Enable the DHCP client by checking this box. If DHCP fails or the
configured IP address is zero, DHCP will retry. If DHCP retry fails,
DHCP will stop trying and the configured IP settings will be used.
IP Address
Assigns the IP address of the network in use. If DHCP client
function is enabled, you do not need to assign the IP address.
The network DHCP server will assign an IP address to the switch
and it will be displayed in this column. The default IP is
192.168.10.1.
IP Mask
Assigns the subnet mask of the IP address. If DHCP client
function is enabled, you do not need to assign the subnet mask.
IP Router
Assigns the network gateway for the switch. The default gateway
is 192.168.10.254.
VLAN ID
Provides the managed VLAN ID. The allowed range is 1 through
4095.
DNS Server
Enter the IP address of the DNS server in dotted decimal notation.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
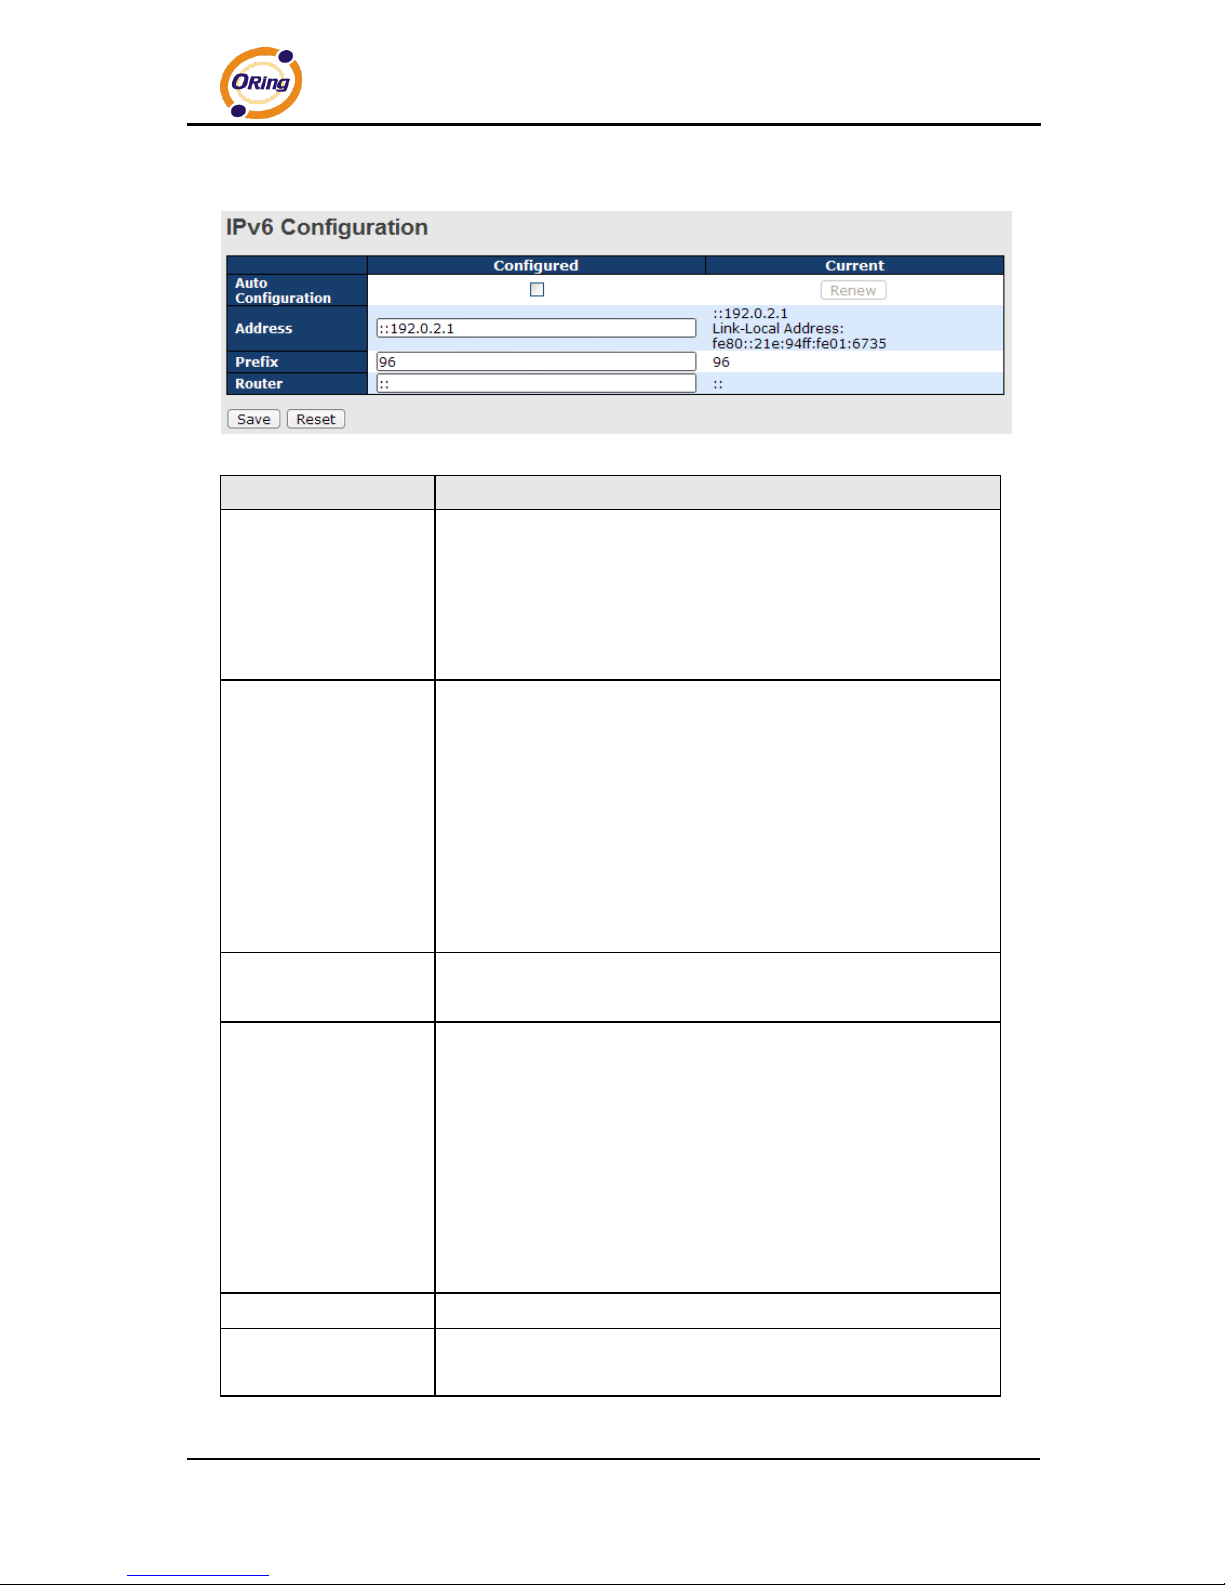
5.1.5 IPv6 Settings
IPv6 is the next-generation IP that uses a 128-bit address standard. It is developed to
supplement, and eventually replace the IPv4 protocol. You can configure IPv6 information of
Page 40
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
39
the switch on the following page.
Label
Description
Auto Configuration
Check to enable IPv6 auto-configuration. If the system cannot
obtain the stateless address in time, the configured IPv6 settings
will be used. The router may delay responding to a router
solicitation for a few seconds; therefore, the total time needed to
complete auto-configuration may be much longer.
Address
Specify an IPv6 address for the switch. IPv6 address consists of
128 bits represented as eight groups of four hexadecimal digits
with a colon separating each field (:). For example, in
'fe80::215:c5ff:fe03:4dc7', the symbol '::' is a special syntax that
can be used as a shorthand way of representing multiple 16-bit
groups of contiguous zeros; but it can appear only once. It can
also represent a legally valid IPv4 address. For example,
'::192.1.2.34'.
Prefix
Specify an IPv6 prefix for the switch. The allowed range is 1 to
128.
Router
Specify an IPv6 address for the switch. IPv6 address consists of
128 bits represented as eight groups of four hexadecimal digits
with a colon separating each field (:). For example, in
'fe80::215:c5ff:fe03:4dc7', the symbol '::' is a special syntax that
can be used as a shorthand way of representing multiple 16-bit
groups of contiguous zeros; but it can appear only once. It can
also represent a legally valid IPv4 address. For example,
'::192.1.2.34'.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
Page 41
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
40
5.1.6 HTTPS
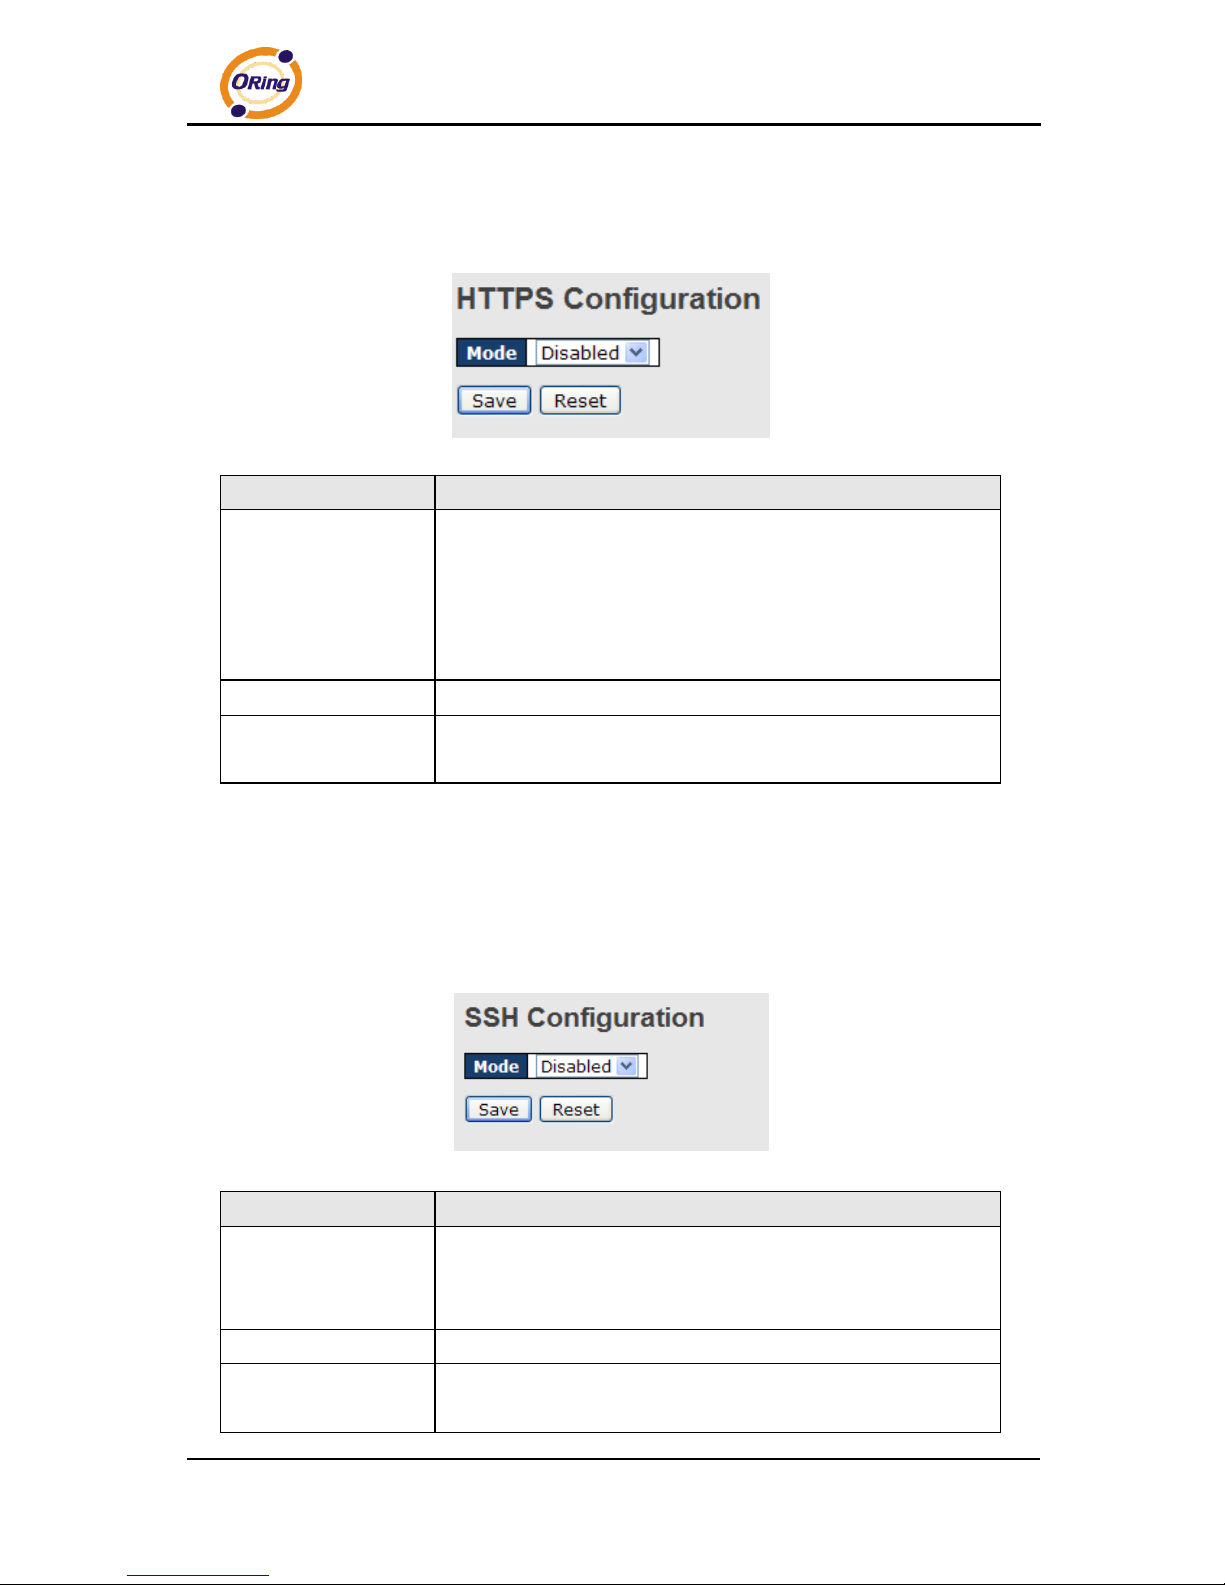
You can configure the HTTPS mode in the following page.
Label
Description
Mode
Indicates the selected HTTPS mode. When the current
connection is HTTPS, disabling HTTPS will automatically redirect
web browser to an HTTP connection. The modes include:
Enabled: enable HTTPS.
Disabled: disable HTTPS.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
5.1.7 SSH
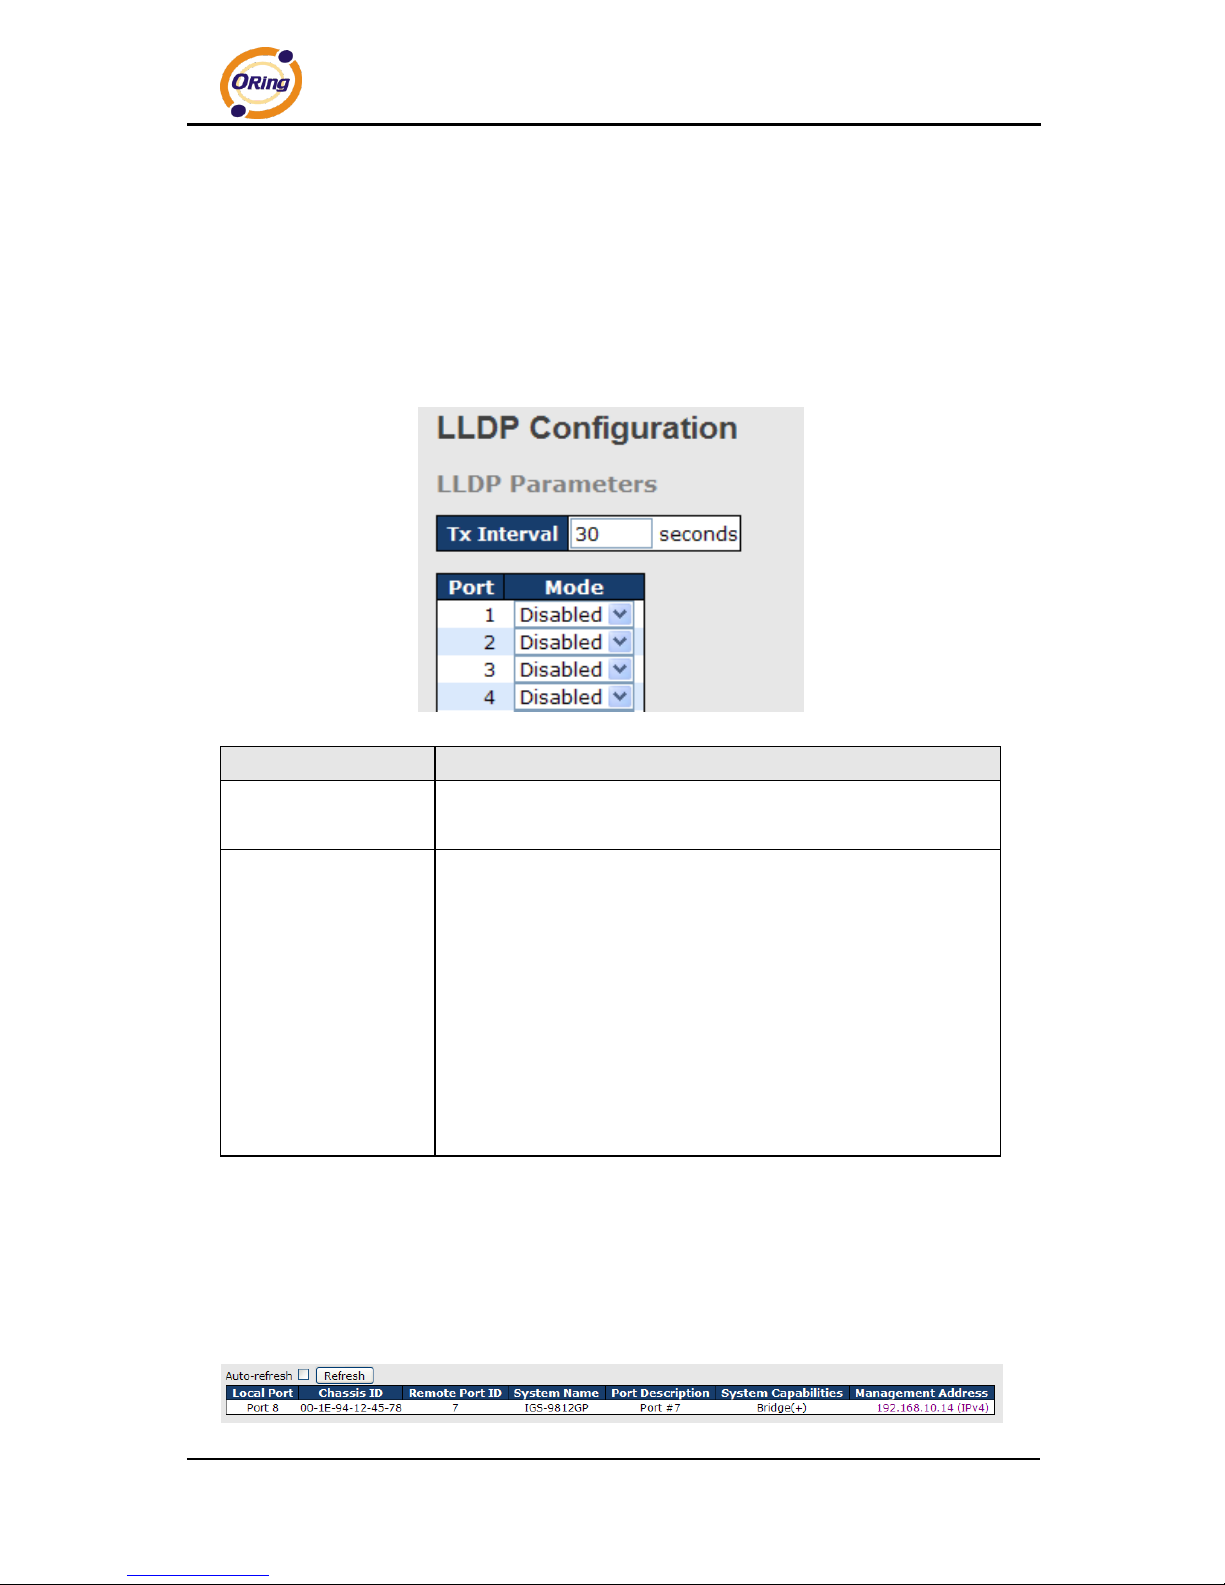
SSH (Secure Shell) is a cryptographic network protocol intended for secure data transmission
and remote access by creating a secure channel between two networked PCs. You can
configure the SSH mode in the following page.
Label
Description
Mode
Indicates the selected SSH mode. The modes include:
Enabled: enable SSH.
Disabled: disable SSH.
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
Page 42
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
41
5.1.8 LLDP
LLDP Configurations
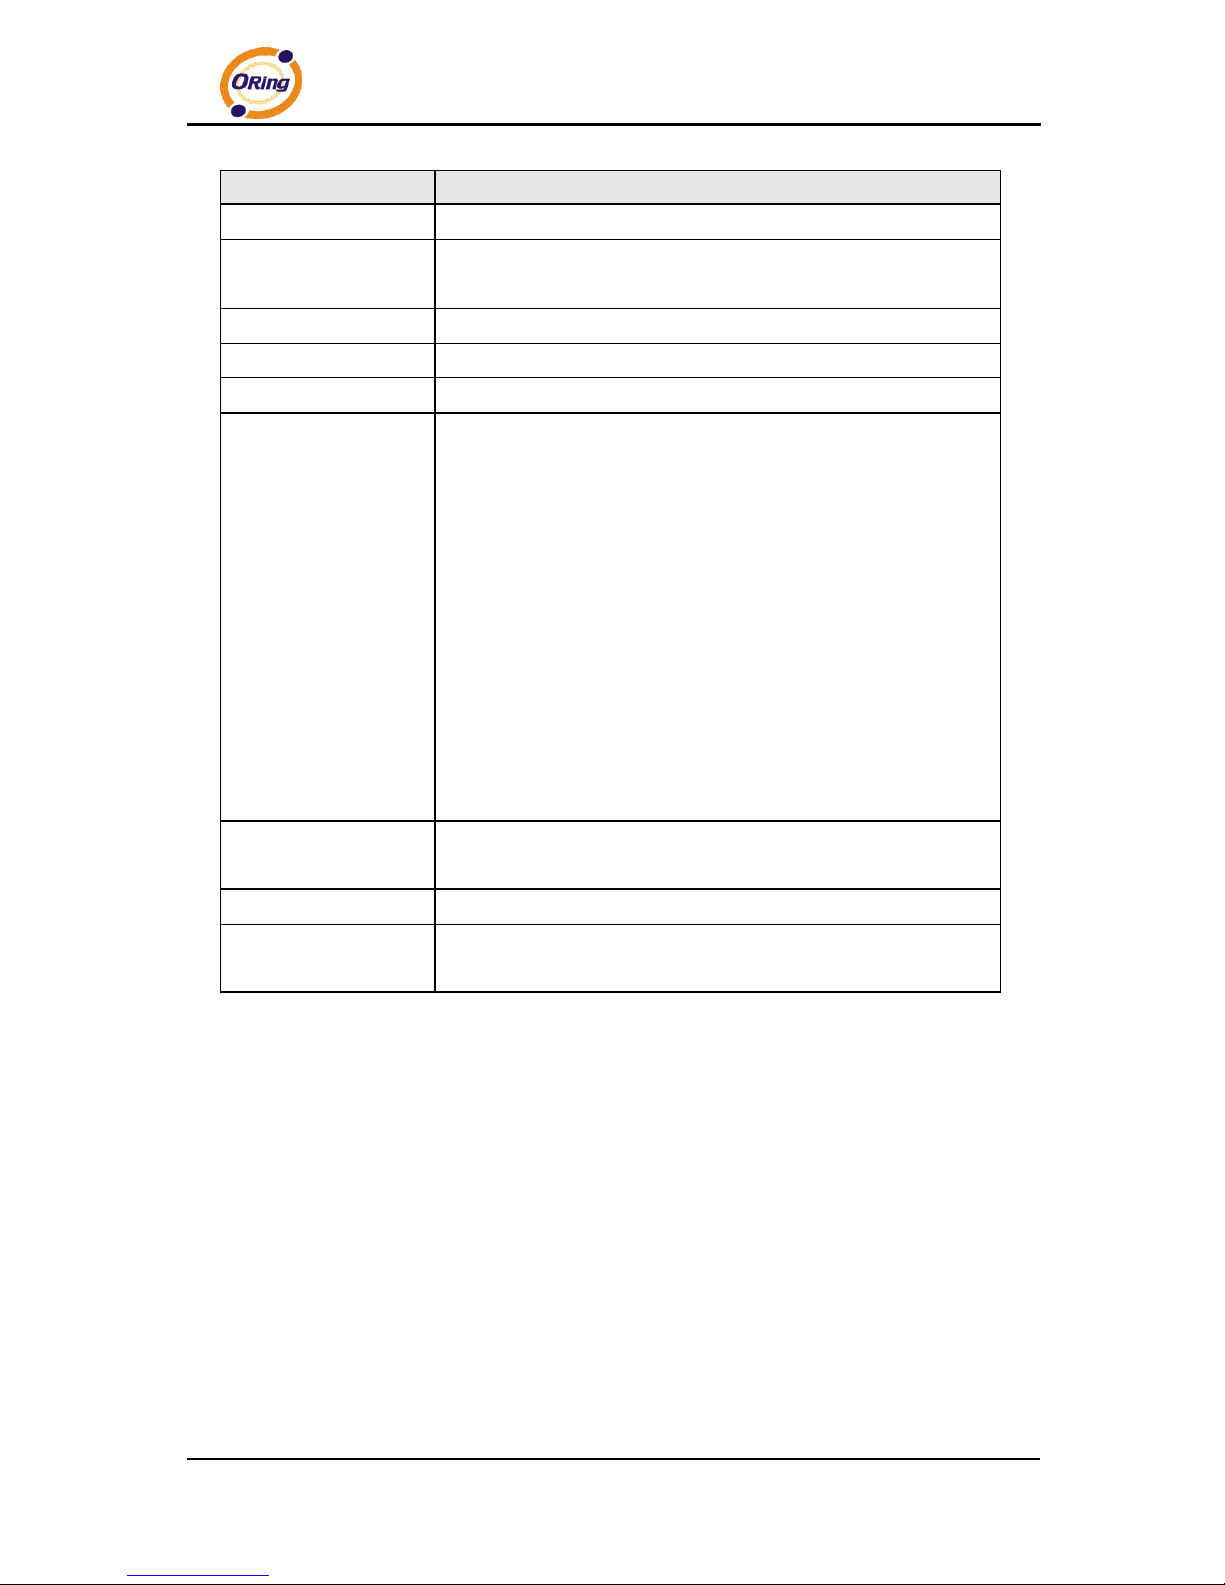
LLDP (Link Layer Discovery Protocol) provides a method for networked devices to receive
and/or transmit their information to other connected devices on the network that are also using
the protocols, and to store the information that is learned about other devices. This page
allows you to examine and configure current LLDP port settings.
Label
Description
Port
The switch port number to which the following settings will be
applied.
Mode
Indicates the selected LLDP mode
Rx only: the switch will not send out LLDP information, but LLDP
information from its neighbors will be analyzed.
Tx only: the switch will drop LLDP information received from its
neighbors, but will send out LLDP information.
Disabled: the switch will not send out LLDP information, and will
drop LLDP information received from its neighbors.
Enabled: the switch will send out LLDP information, and will
analyze LLDP information received from its neighbors.
LLDP Neighbor Information
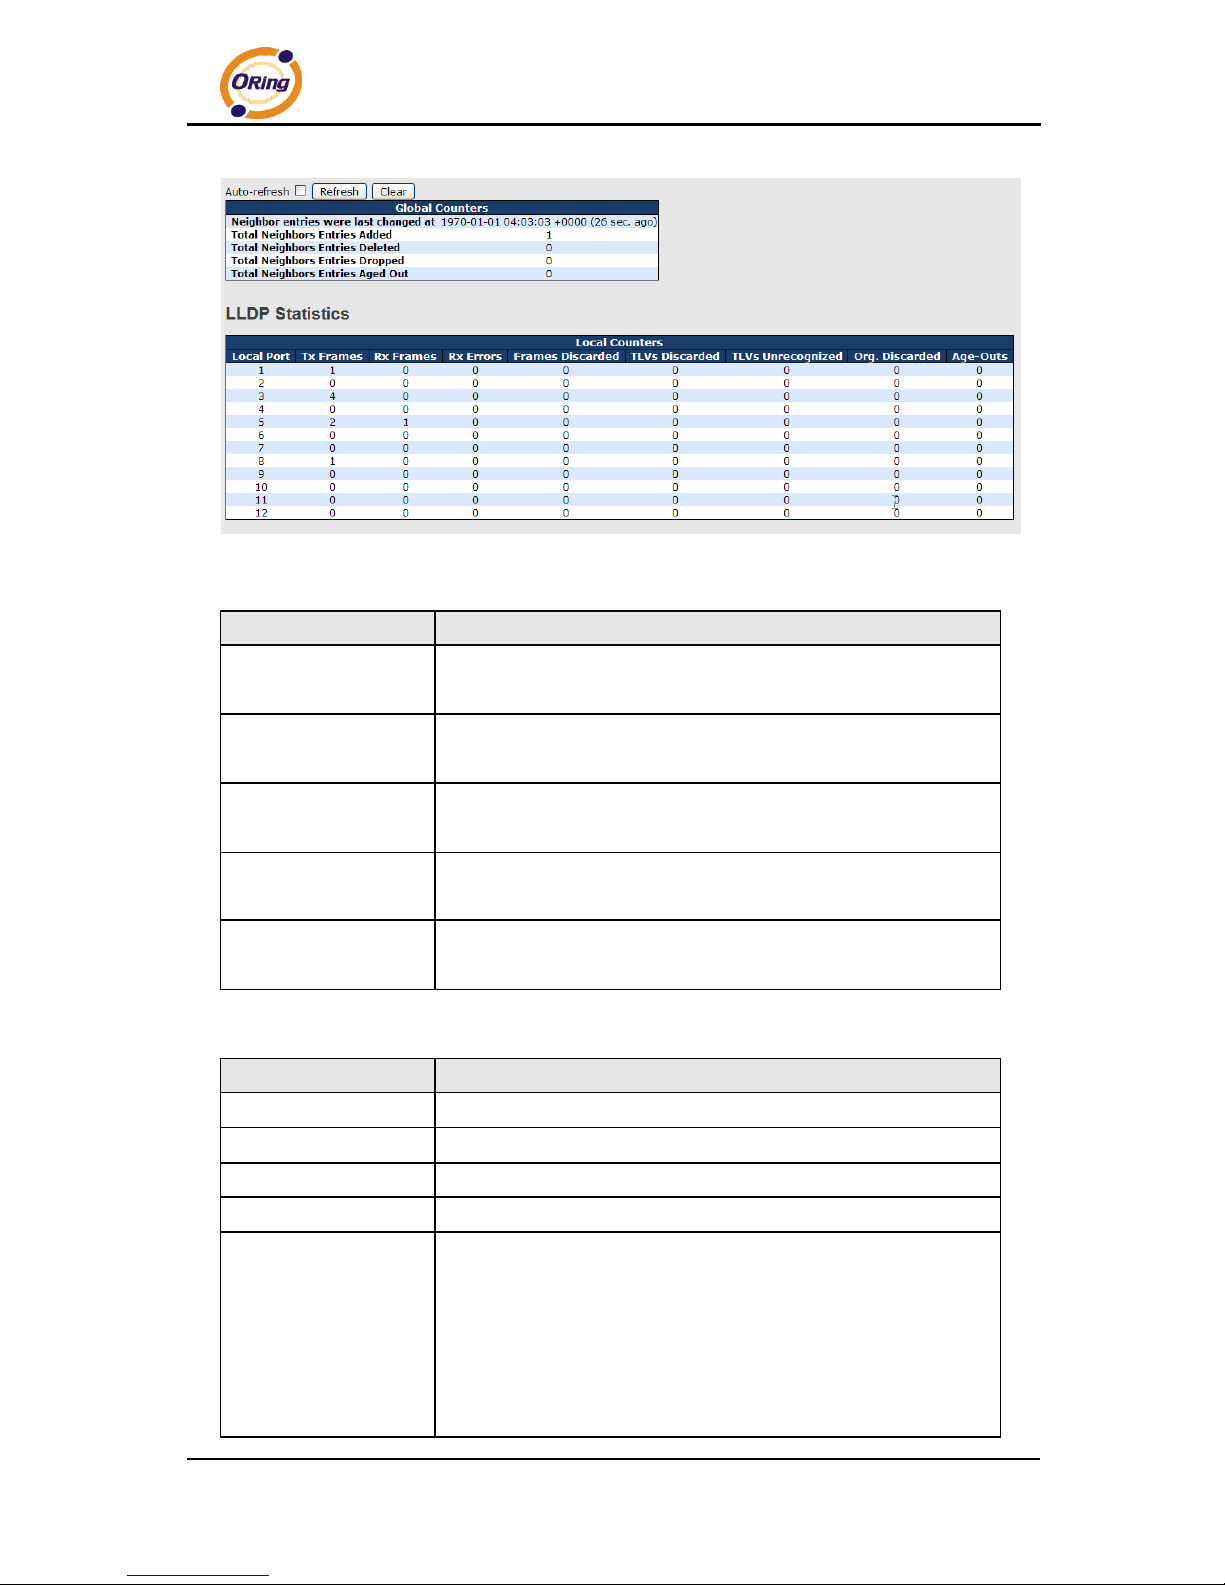
This page provides a status overview for all LLDP neighbors. The following table contains
information for each port on which an LLDP neighbor is detected. The columns include the
following information:
Page 43
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
42
Label
Description
Local Port
The port that you use to transmits and receives LLDP frames.
Chassis ID
The identification number of the neighbor sending out the LLDP
frames.
Remote Port ID
The identification of the neighbor port
System Name
The name advertised by the neighbor.
Port Description
The description of the port advertised by the neighbor.
System Capabilities
Description of the neighbor's capabilities. The capabilities include:
1. Other
2. Repeater
3. Bridge
4. WLAN Access Point
5. Router
6. Telephone
7. DOCSIS Cable Device
8. Station Only
9. Reserved
When a capability is enabled, a (+) will be displayed. If the
capability is disabled, a (-) will be displayed.
Management
Address
The neighbor's address which can be used to help network
management. This may contain the neighbor's IP address.
Refresh
Click to refresh the page immediately
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
LLDP Statistics
This page provides an overview of all LLDP traffic. Two types of counters are shown. Global
counters will apply settings to the whole switch stack, while local counters will apply settings to
specified switches.
Page 44
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
43
Global Counters
Label
Description
Neighbor entries
were last changed at
Shows the time when the last entry was deleted or added.
Total Neighbors
Entries Added
Shows the number of new entries added since switch reboot
Total Neighbors
Entries Deleted
Shows the number of new entries deleted since switch reboot
Total Neighbors
Entries Dropped
Shows the number of LLDP frames dropped due to full entry table
Total Neighbors
Entries Aged Out
Shows the number of entries deleted due to expired time-to-live
Local Counters
Label
Description
Local Port
The port that receives or transmits LLDP frames
Tx Frames
The number of LLDP frames transmitted on the port
Rx Frames
The number of LLDP frames received on the port
Rx Errors
The number of received LLDP frames containing errors
Frames Discarded
If a port receives an LLDP frame, and the switch's internal table is
full, the LLDP frame will be counted and discarded. This situation
is known as "too many neighbors" in the LLDP standard. LLDP
frames require a new entry in the table if Chassis ID or Remote
Port ID is not included in the table. Entries are removed from the
table when a given port links down, an LLDP shutdown frame is
Page 45
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
44
received, or when the entry ages out.
TLVs Discarded
Each LLDP frame can contain multiple pieces of information,
known as TLVs (Type Length Value). If a TLV is malformed, it will
be counted and discarded.
TLVs Unrecognized
The number of well-formed TLVs, but with an unknown type value
Org. Discarded
The number of organizationally TLVs received
Age-Outs
Each LLDP frame contains information about how long the LLDP
information is valid (age-out time). If no new LLDP frame is
received during the age-out time, the LLDP information will be
removed, and the value of the age-out counter will be
incremented.
Refresh
Click to refresh the page immediately
Clear
Click to clear the local counters. All counters (including global
counters) are cleared upon reboot.
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
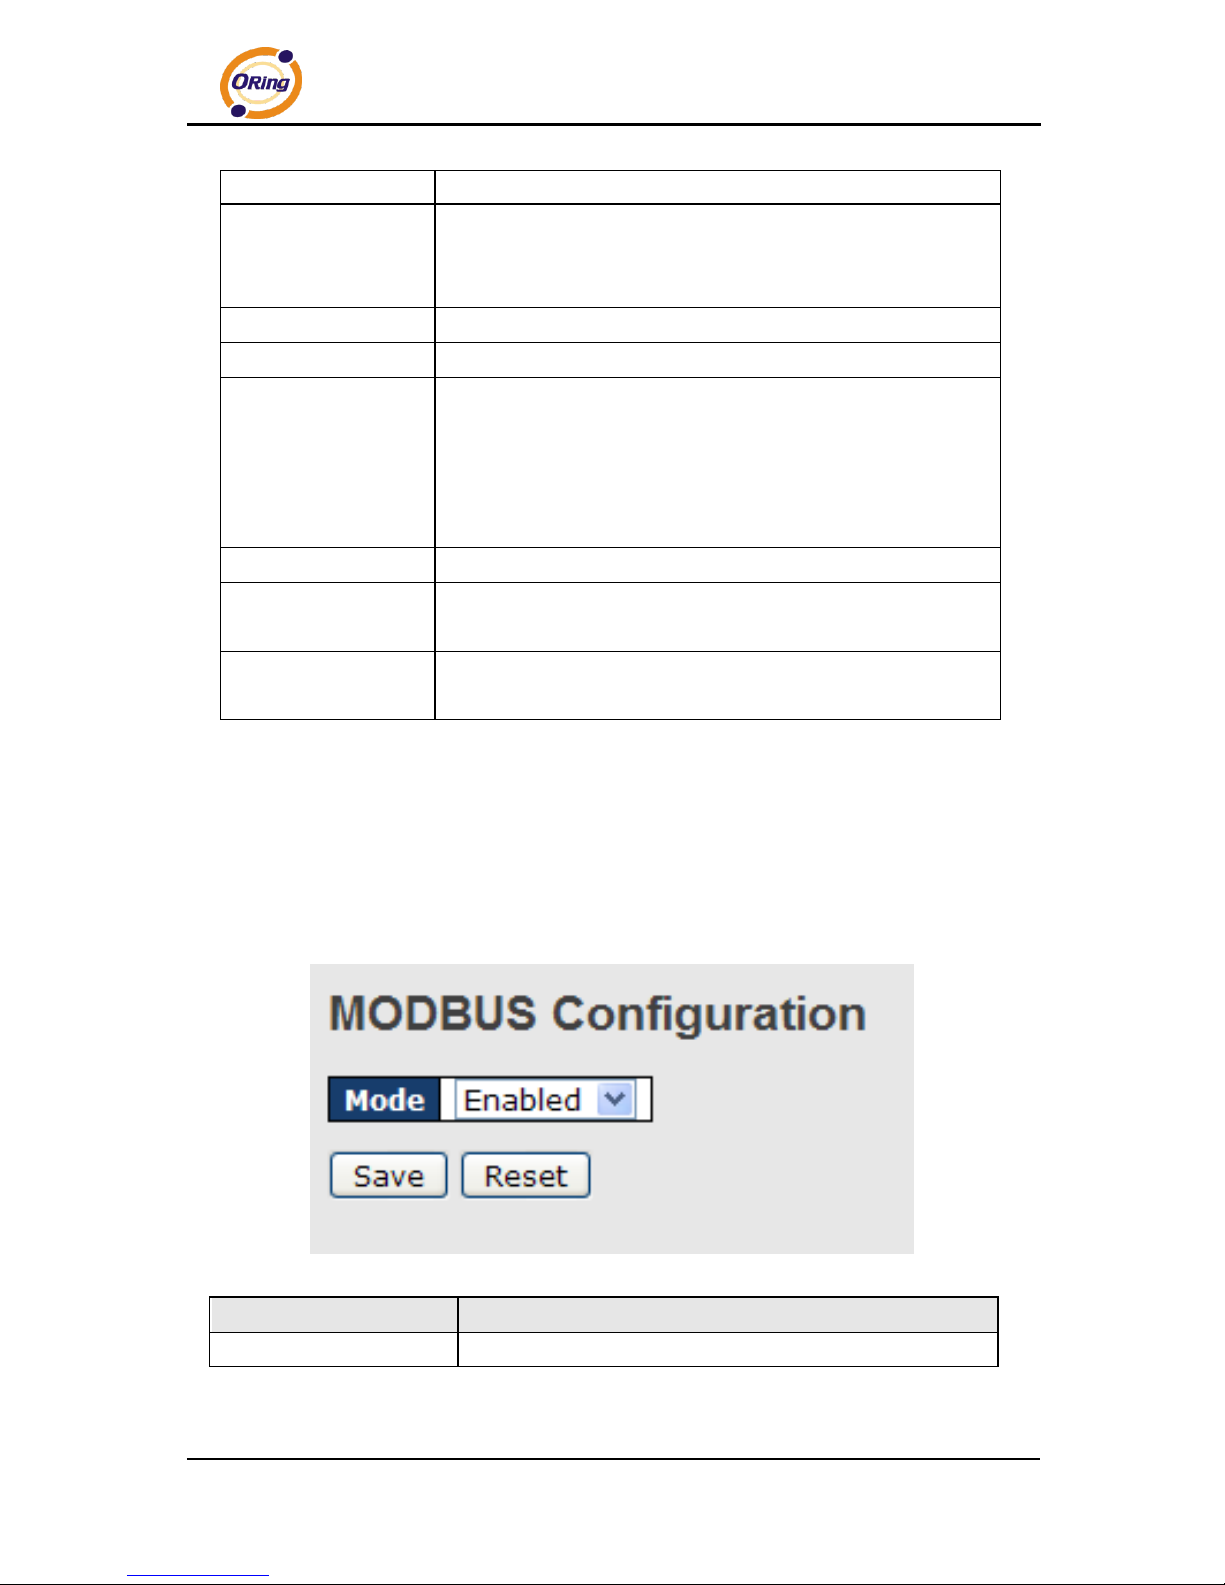
5.1.9 Modbus TCP
Modbus TCP uses TCP/IP and Ethernet to carry the data of the Modbus message structure
between compatible devices. The protocol is commonly used in SCADA systems for
communications between a human-machine interface (HMI) and programmable logic
controllers. This page enables you to enable and disable Modbus TCP support of the switch.
Label
Description
Mode
Shows the existing status of the Modbus TCP function
Page 46
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
45
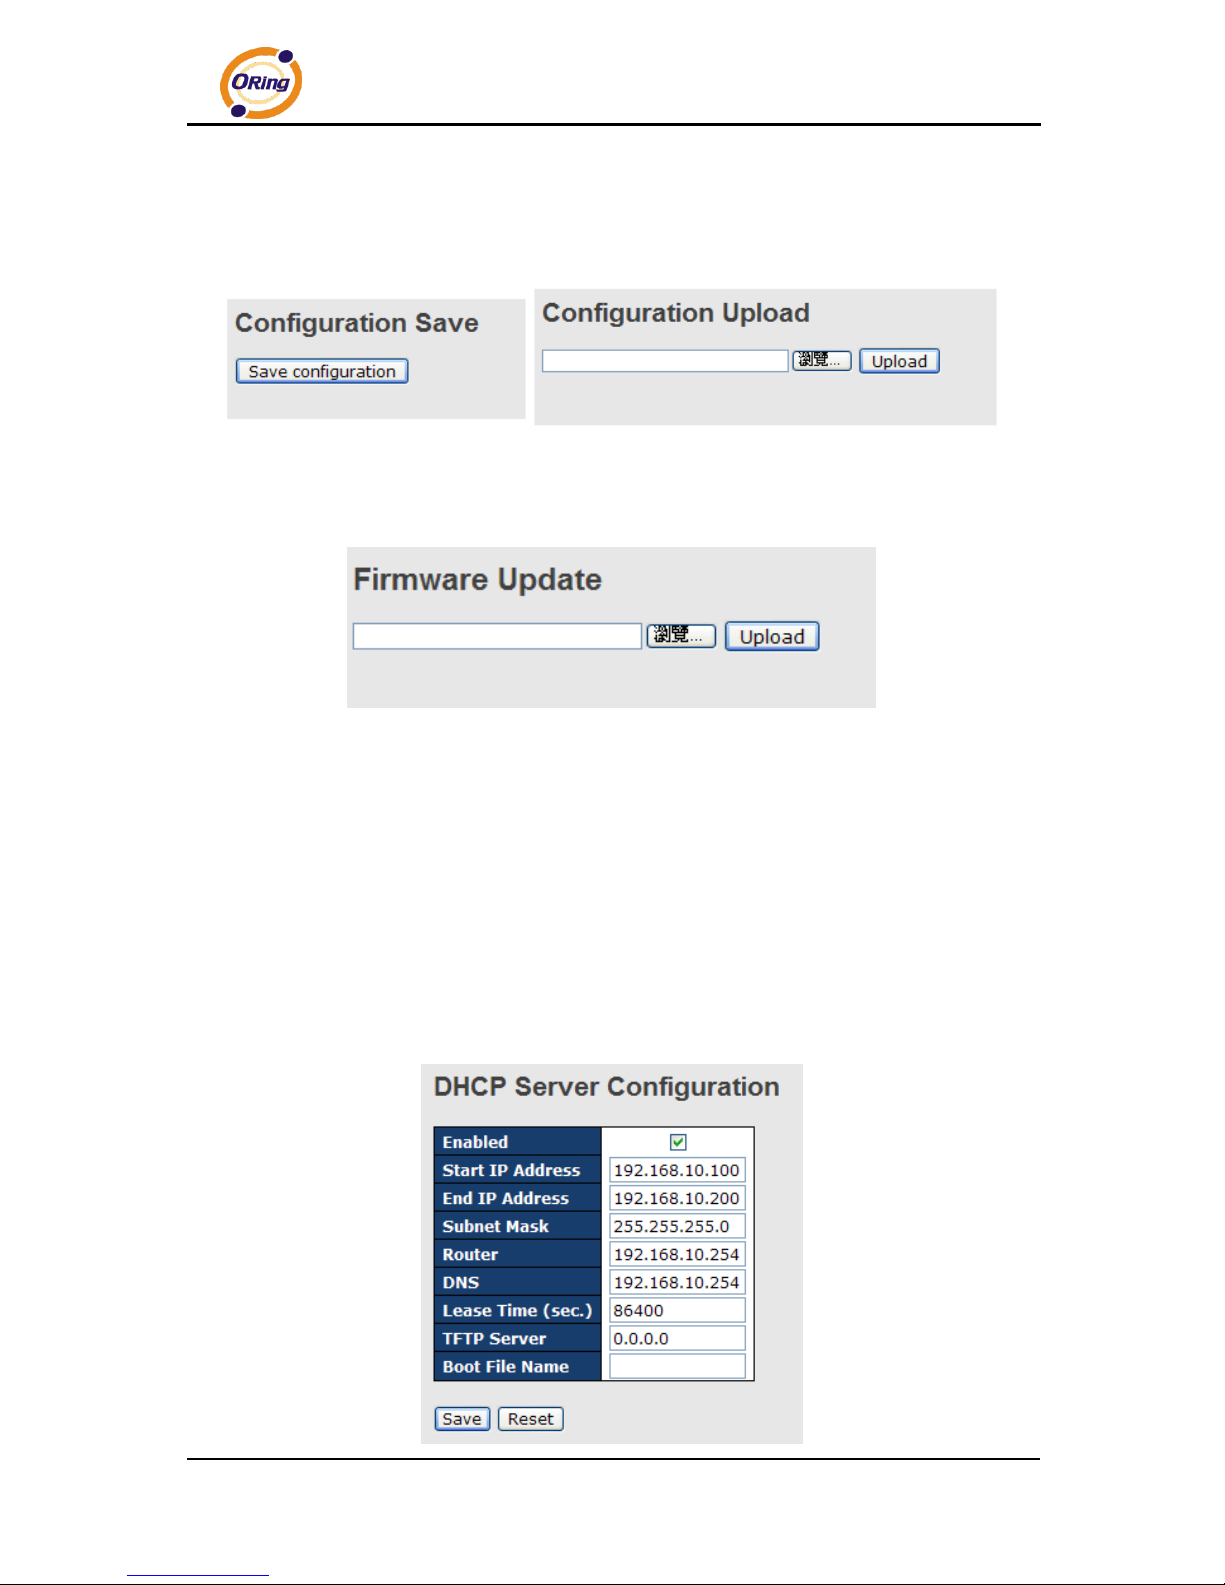
5.1.10 Backup/Restore Configurations
You can save/view or load switch configurations through the following pages. The
configuration file is in XML format.
5.1.11 Firmware Update
This page allows you to update the firmware of the switch.
5.2 DHCP Server
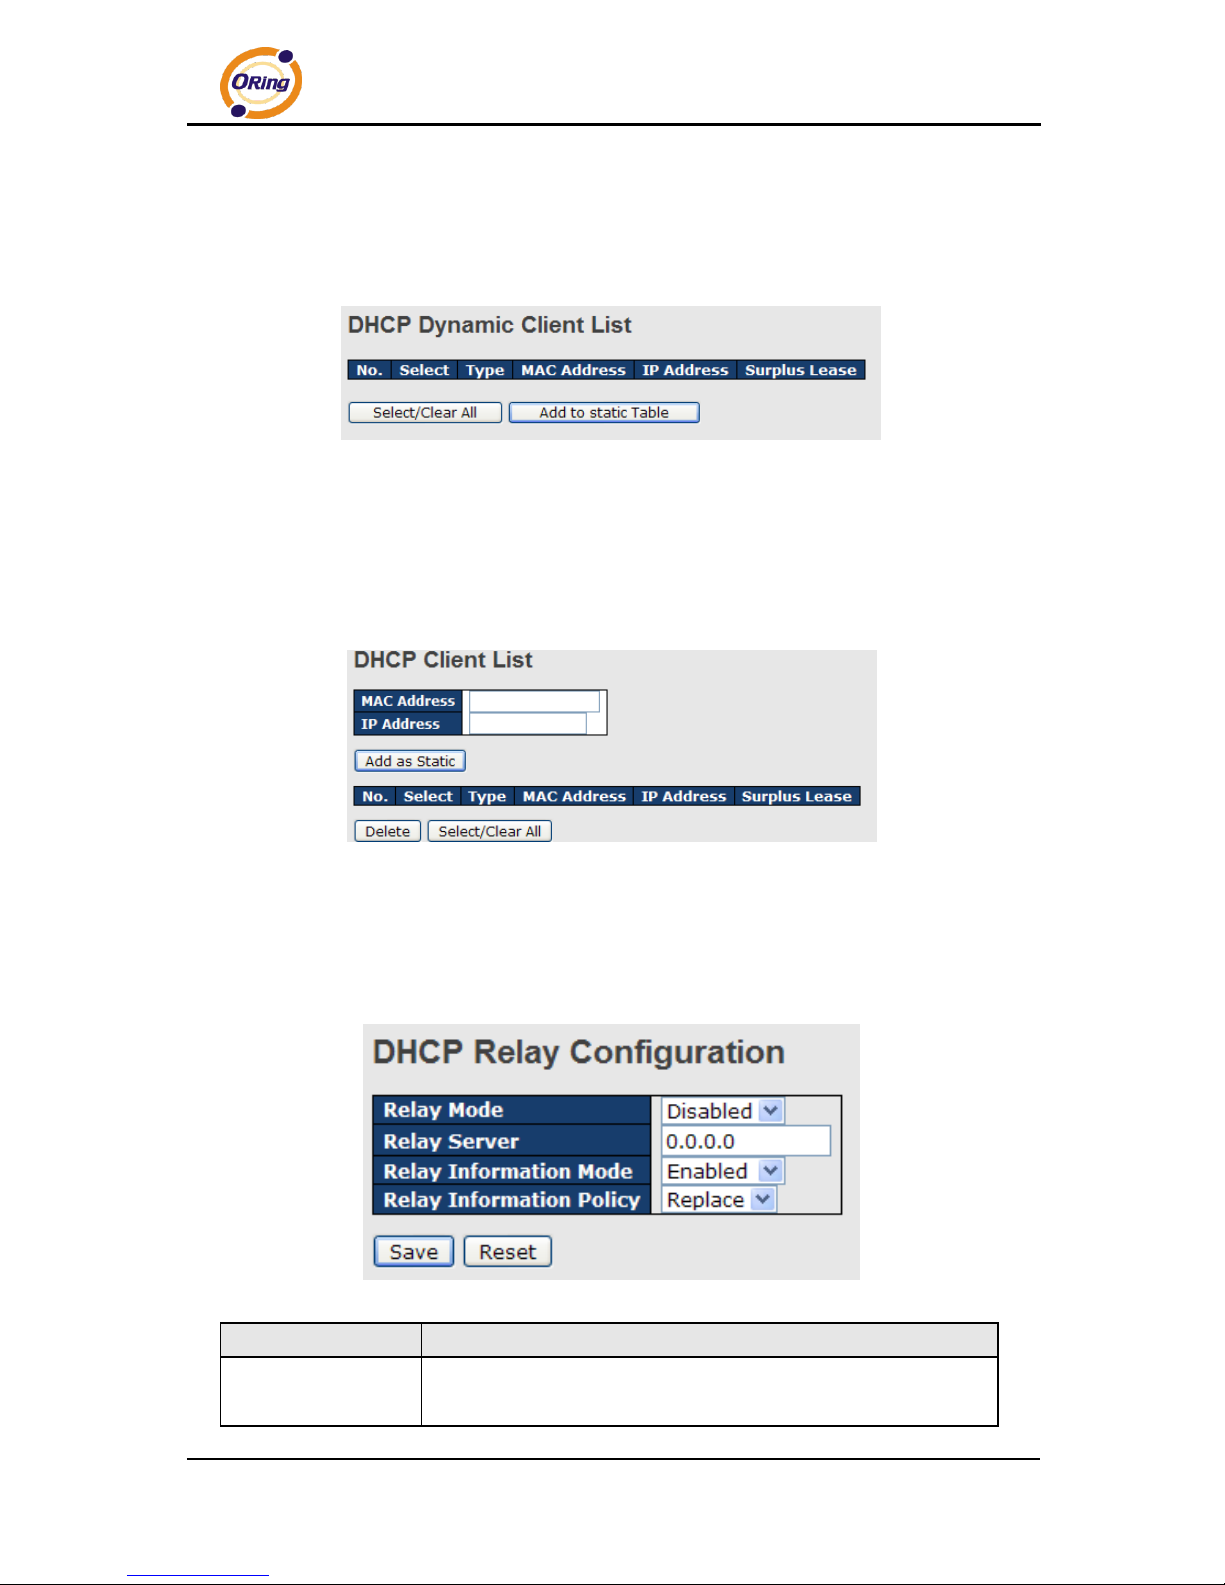
The switch provides DHCP server functions. By enabling DHCP, the switch will become a
DHCP server and dynamically assigns IP addresses and related IP information to network
clients.
5.2.1 Basic Settings
This page allows you to set up DHCP settings for the switch. You can check the Enabled
checkbox to activate the function. Once the box is checked, you will be able to input
information in each column.
Page 47
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
46
5.2.2 Dynamic Client List
When DHCP server functions are activated, the switch will collect DHCP client information and
display in the following table.
5.2.3 Client List
You can assign a specific IP address within the dynamic IP range to a specific port. When a
device is connected to the port and requests for dynamic IP assigning, the switch will assign
the IP address that has previously been assigned to the connected device.
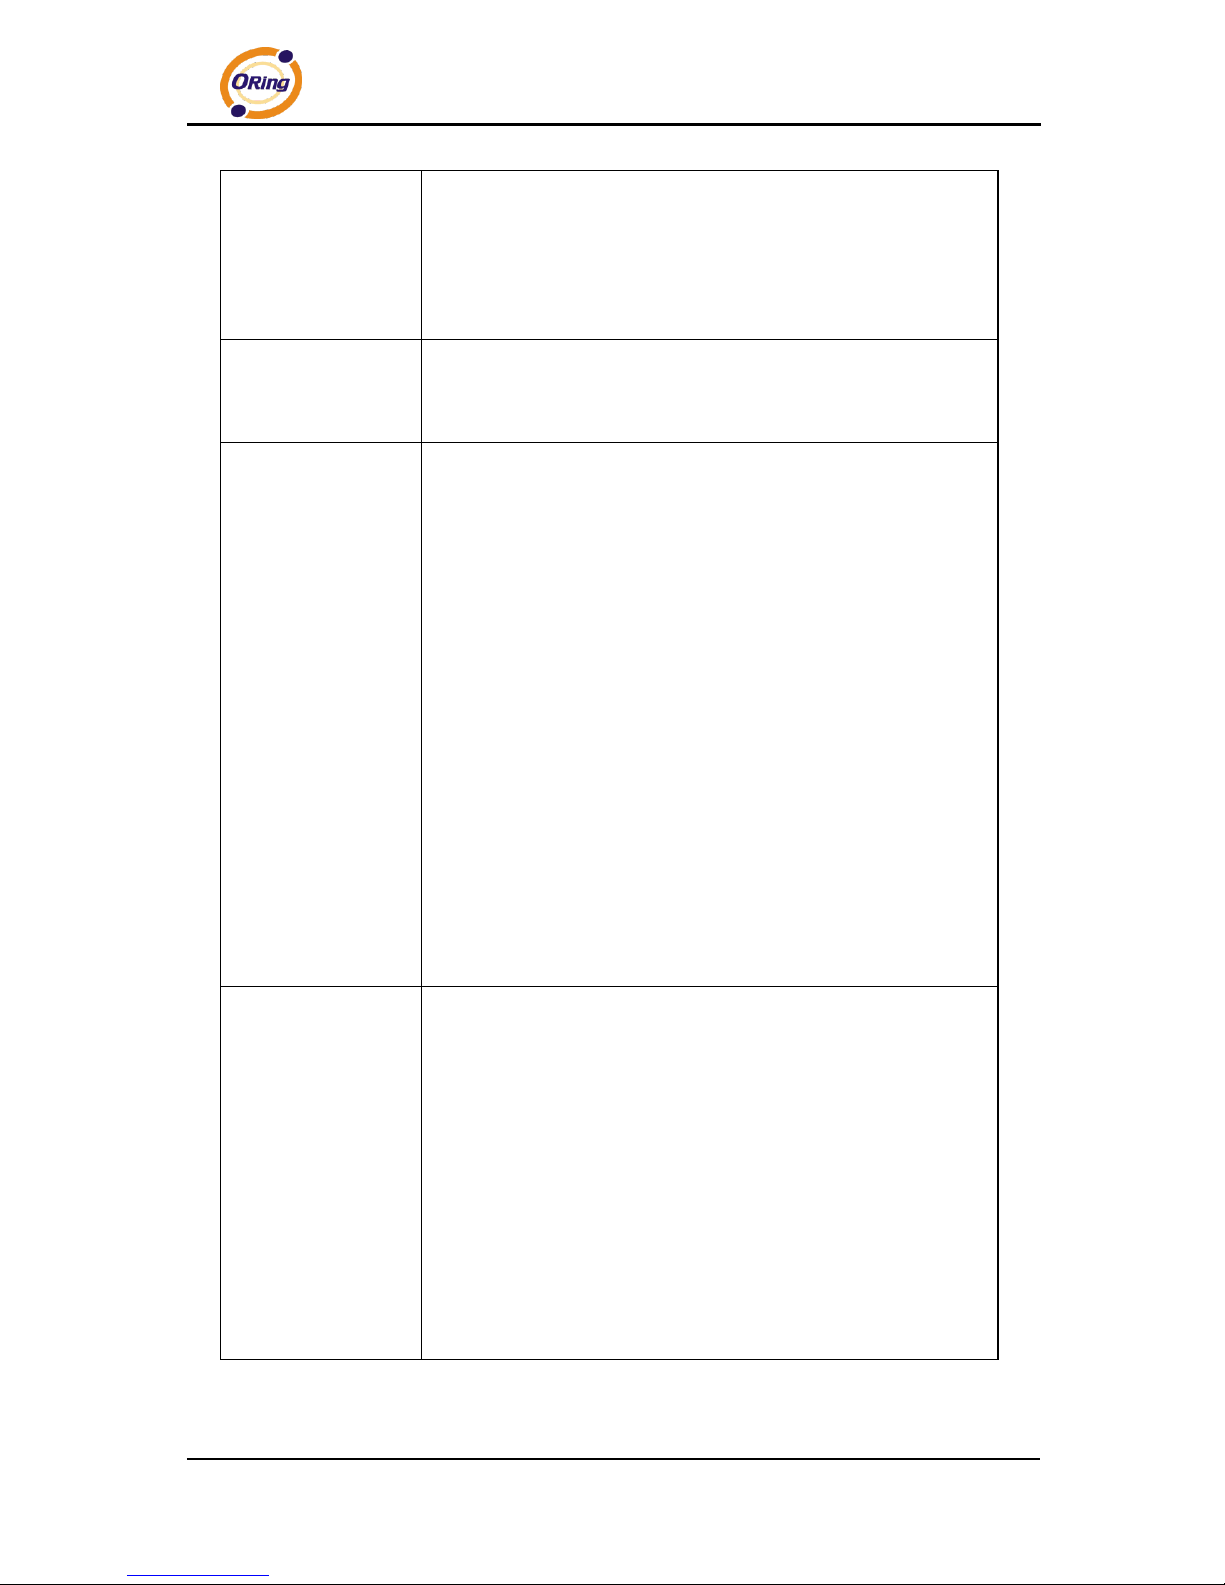
5.2.4 DHCP Relay
DHCP relay is used to forward and transfer DHCP messages between the clients and the
server when they are not in the same subnet domain. You can configure the function in this
page.
Label
Description
Relay Mode
Indicates the existing DHCP relay mode. The modes include:
Enabled: activate DHCP relay. When DHCP relay is enabled, the
Page 48
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
47
agent forwards and transfers DHCP messages between the clients
and the server when they are not in the same subnet domain to
prevent the DHCP broadcast message from flooding for security
considerations.
Disabled: disable DHCP relay
Relay Server
Indicates the DHCP relay server IP address. A DHCP relay agent is
used to forward and transfer DHCP messages between the clients
and the server when they are not in the same subnet domain.
Relay Information
Mode
Indicates the existing DHCP relay information mode. The format of
DHCP option 82 circuit ID format is "[vlan_id][module_id][port_no]".
The first four characters represent the VLAN ID, and the fifth and
sixth characters are the module ID. In stand-alone devices, the
module ID always equals to 0; in stacked devices, it means switch
ID. The last two characters are the port number. For example,
"00030108" means the DHCP message received form VLAN ID 3,
switch ID 1, and port No. 8. The option 82 remote ID value equals
to the switch MAC address.
The modes include:
Enabled: activate DHCP relay information. When DHCP relay
information is enabled, the agent inserts specific information
(option 82) into a DHCP message when forwarding to a DHCP
server and removes it from a DHCP message when transferring to
a DHCP client. It only works when DHCP relay mode is enabled.
Disabled: disable DHCP relay information
Relay Information
Policy
Indicates the policies to be enforced when receiving DHCP relay
information. When DHCP relay information mode is enabled, if the
agent receives a DHCP message that already contains relay agent
information, it will enforce the policy. The Replace option is invalid
when relay information mode is disabled. The policies includes:
Replace: replace the original relay information when a DHCP
message containing the information is received.
Keep: keep the original relay information when a DHCP message
containing the information is received.
Drop: drop the package when a DHCP message containing the
information is received.
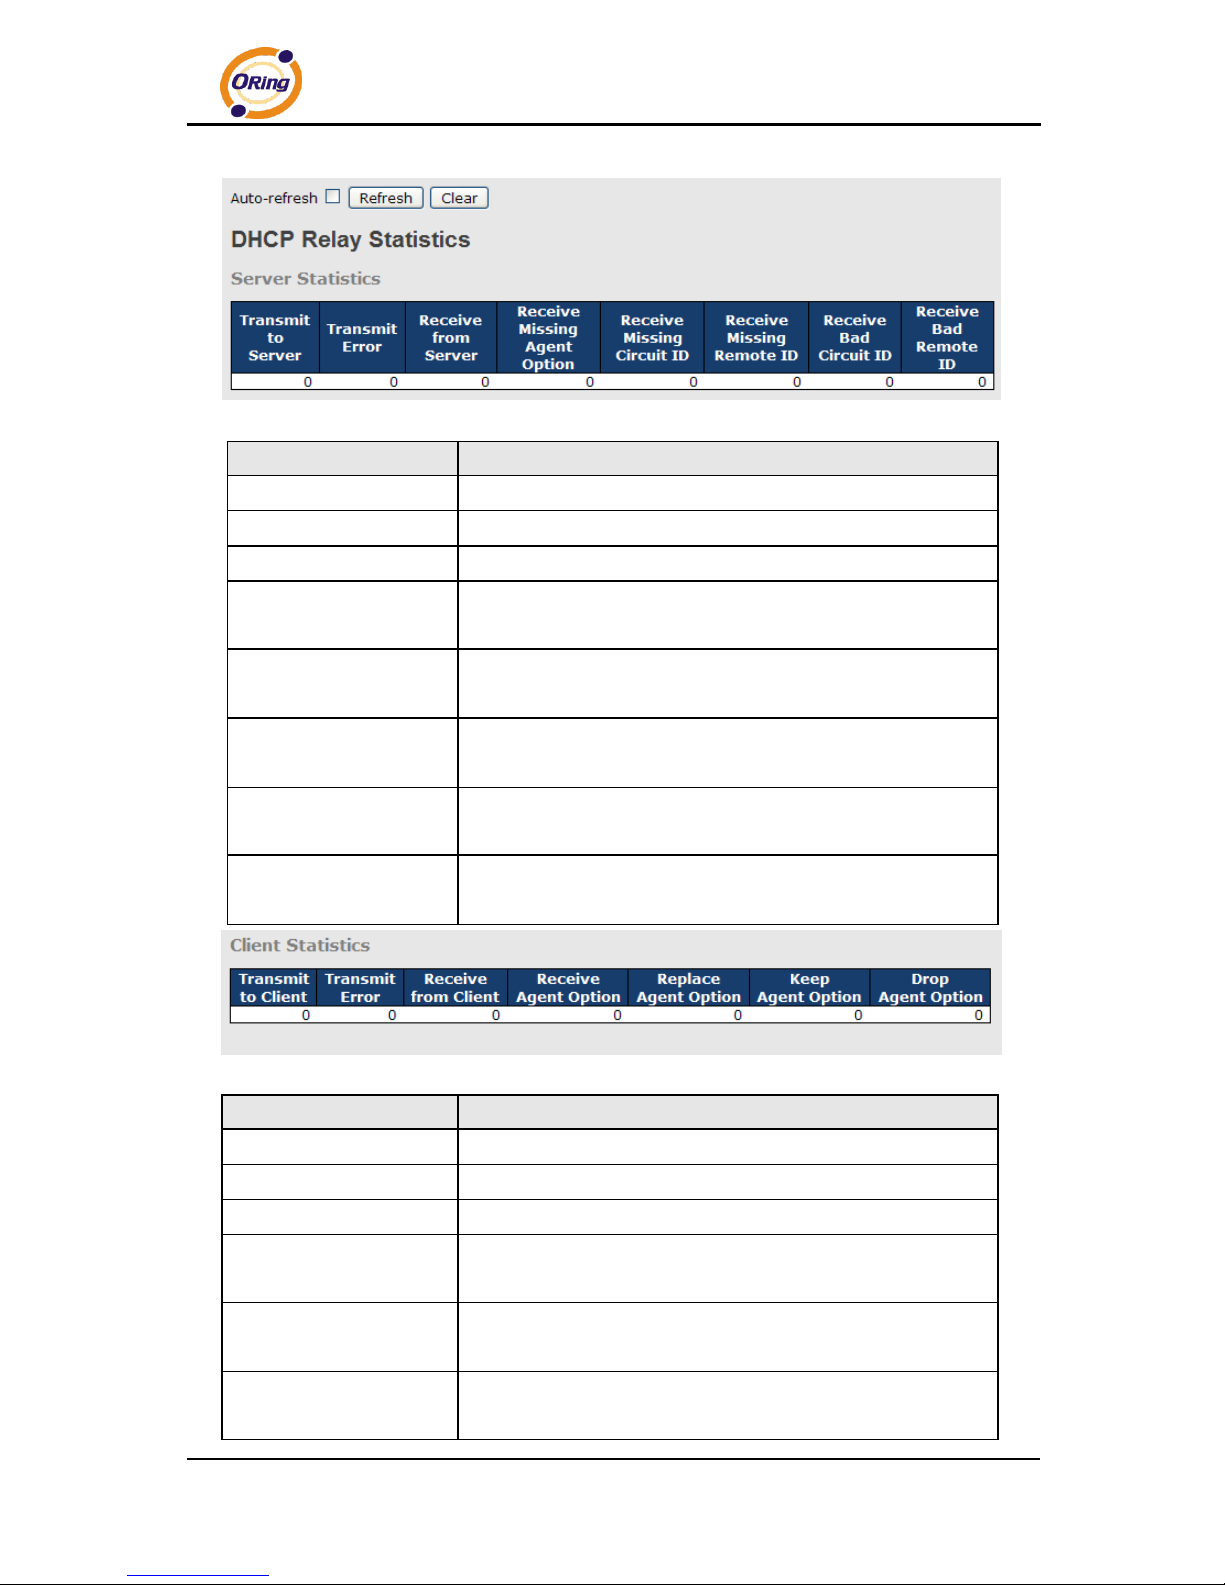
The relay statistics shows the information of relayed packets of the switch.
Page 49
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
48
Label
Description
Transmit to Sever
The number of packets relayed from the client to the server
Transmit Error
The number of packets with errors when being sent to clients
Receive from Server
The number of packets received from the server
Receive Missing Agent
Option
The number of packets received without agent information
Receive Missing
Circuit ID
The number of packets received with Circuit ID
Receive Missing
Remote ID
The number of packets received with the Remote ID option
missing.
Receive Bad Circuit ID
The number of packets whose Circuit ID do not match the
known circuit ID
Receive Bad Remote ID
The number of packets whose Remote ID do not match the
known Remote ID
Label
Description
Transmit to Client
The number of packets relayed from the server to the client
Transmit Error
The number of packets with errors when being sent to servers
Receive from Client
The number of packets received from the server
Receive Agent Option
The number of received packets containing relay agent
information
Replace Agent Option
The number of packets replaced when received messages
contain relay agent information.
Keep Agent Option
The number of packets whose relay agent information is
retained
Page 50
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
49
Drop Agent Option
The number of packets dropped when received messages
contain relay agent information.
5.3 Port Setting
Port Setting allows you to manage individual ports of the switch, including traffic, power, and
trunks.
5.3.1 Port Control
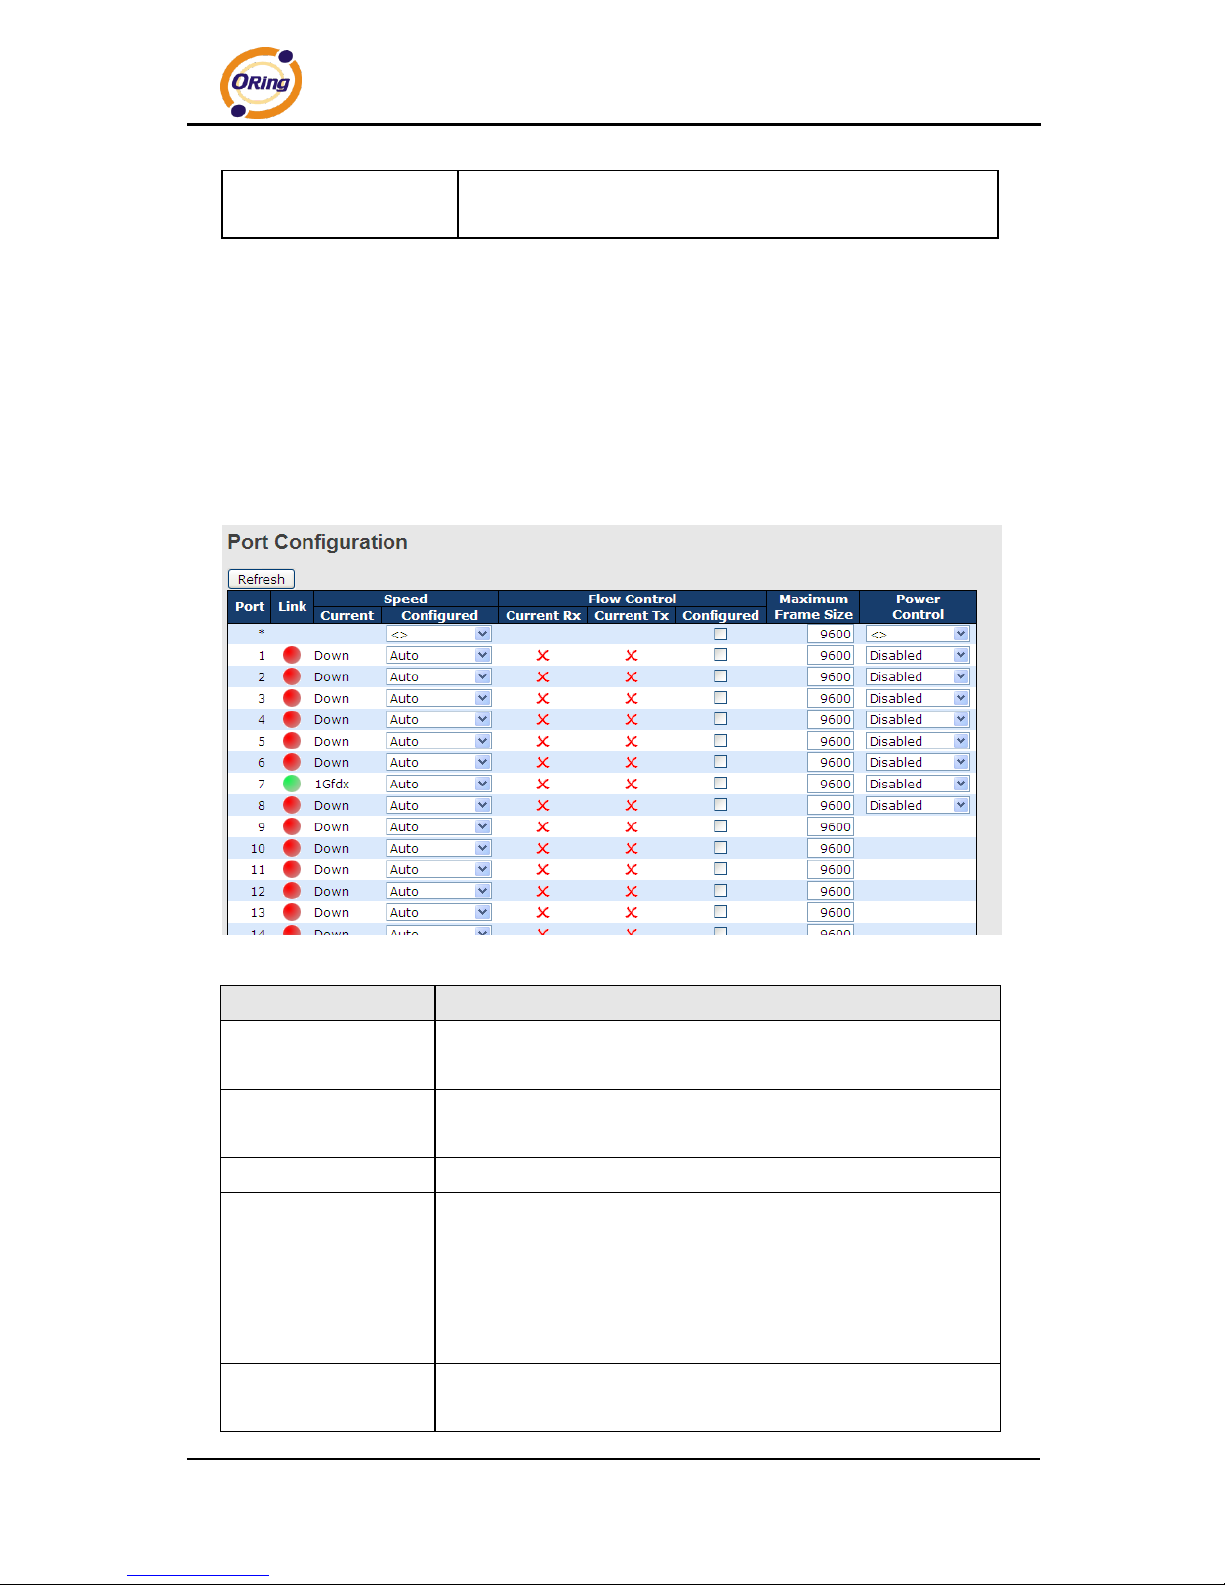
This page shows current port configurations. Ports can also be configured here.
Label
Description
Port
The switch port number to which the following settings will be
applied.
Link
The current link state is shown by different colors. Green indicates
the link is up and red means the link is down.
Current Link Speed
Indicates the current link speed of the port
Configured Link
Speed
The drop-down list provides available link speed options for a
given switch port
Auto selects the highest speed supported by the link partner
Disabled disables switch port configuration
<> configures all ports
Flow Control
When Auto is selected for the speed, the flow control will be
negotiated to the capacity advertised by the link partner.
Page 51
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
50
When a fixed-speed setting is selected, that is what is used.
Current Rx indicates whether pause frames on the port are
obeyed, and Current Tx indicates whether pause frames on the
port are transmitted. The Rx and Tx settings are determined by
the result of the last auto-negotiation.
You can check the Configured column to use flow control. This
setting is related to the setting of Configured Link Speed.
Maximum Frame
You can enter the maximum frame size allowed for the switch port
in this column, including FCS. The allowed range is 1518 bytes to
9600 bytes.
Power Control
Shows the current power consumption of each port in percentage.
The Configured column allows you to change power saving
parameters for each port.
Disabled: all power savings functions are disabled
ActiPHY: link down and power savings enabled
PerfectReach: link up and power savings enabled
Enabled: both link up and link down power savings enabled
Total Power Usage
Total power consumption of the board, measured in percentage
Save
Click to save changes
Reset
Click to undo any changes made locally and revert to previously
saved values
Refresh
Click to refresh the page. Any changes made locally will be
undone.
5.3.2 Port Trunk
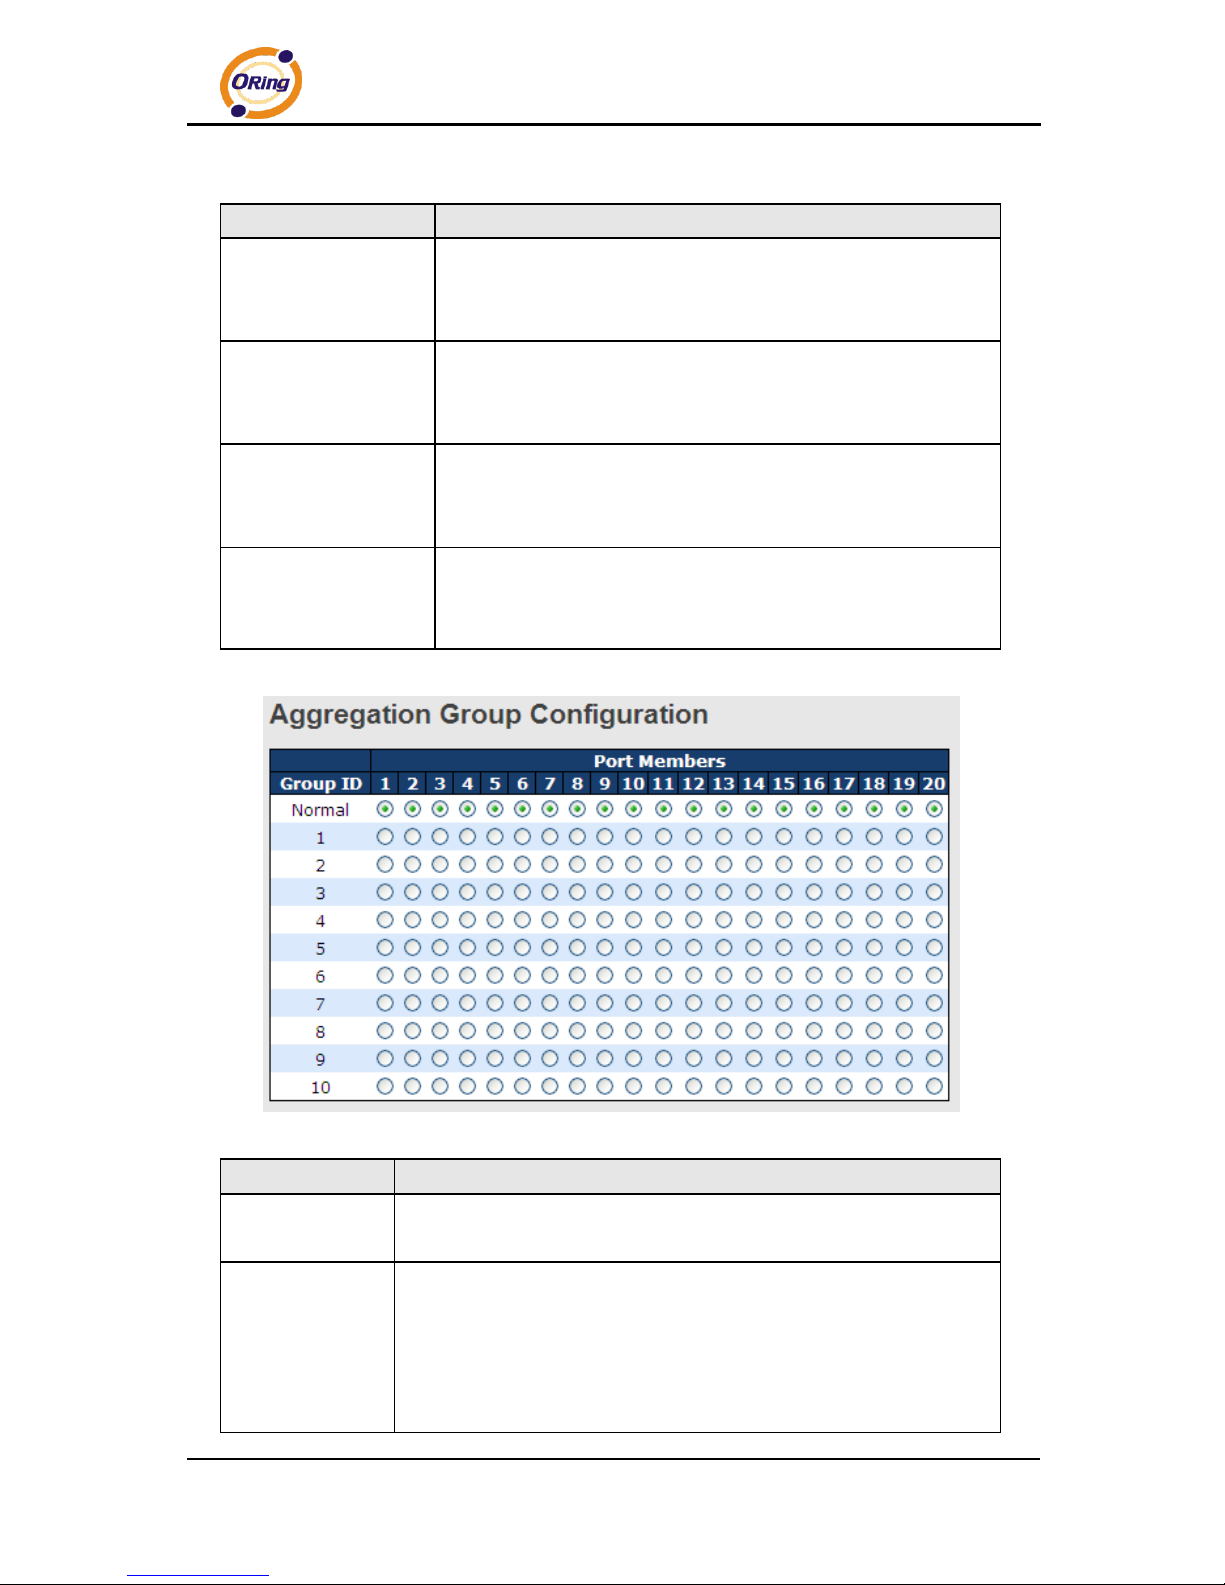
A port trunk is a group of ports that have been grouped together to function as one logical path.
This method provides an economical way for you to increase the bandwidth between the
switch and another networking device. In addition, it is useful when a single physical link
between the devices is insufficient to handle the traffic load. This page allows you to configure
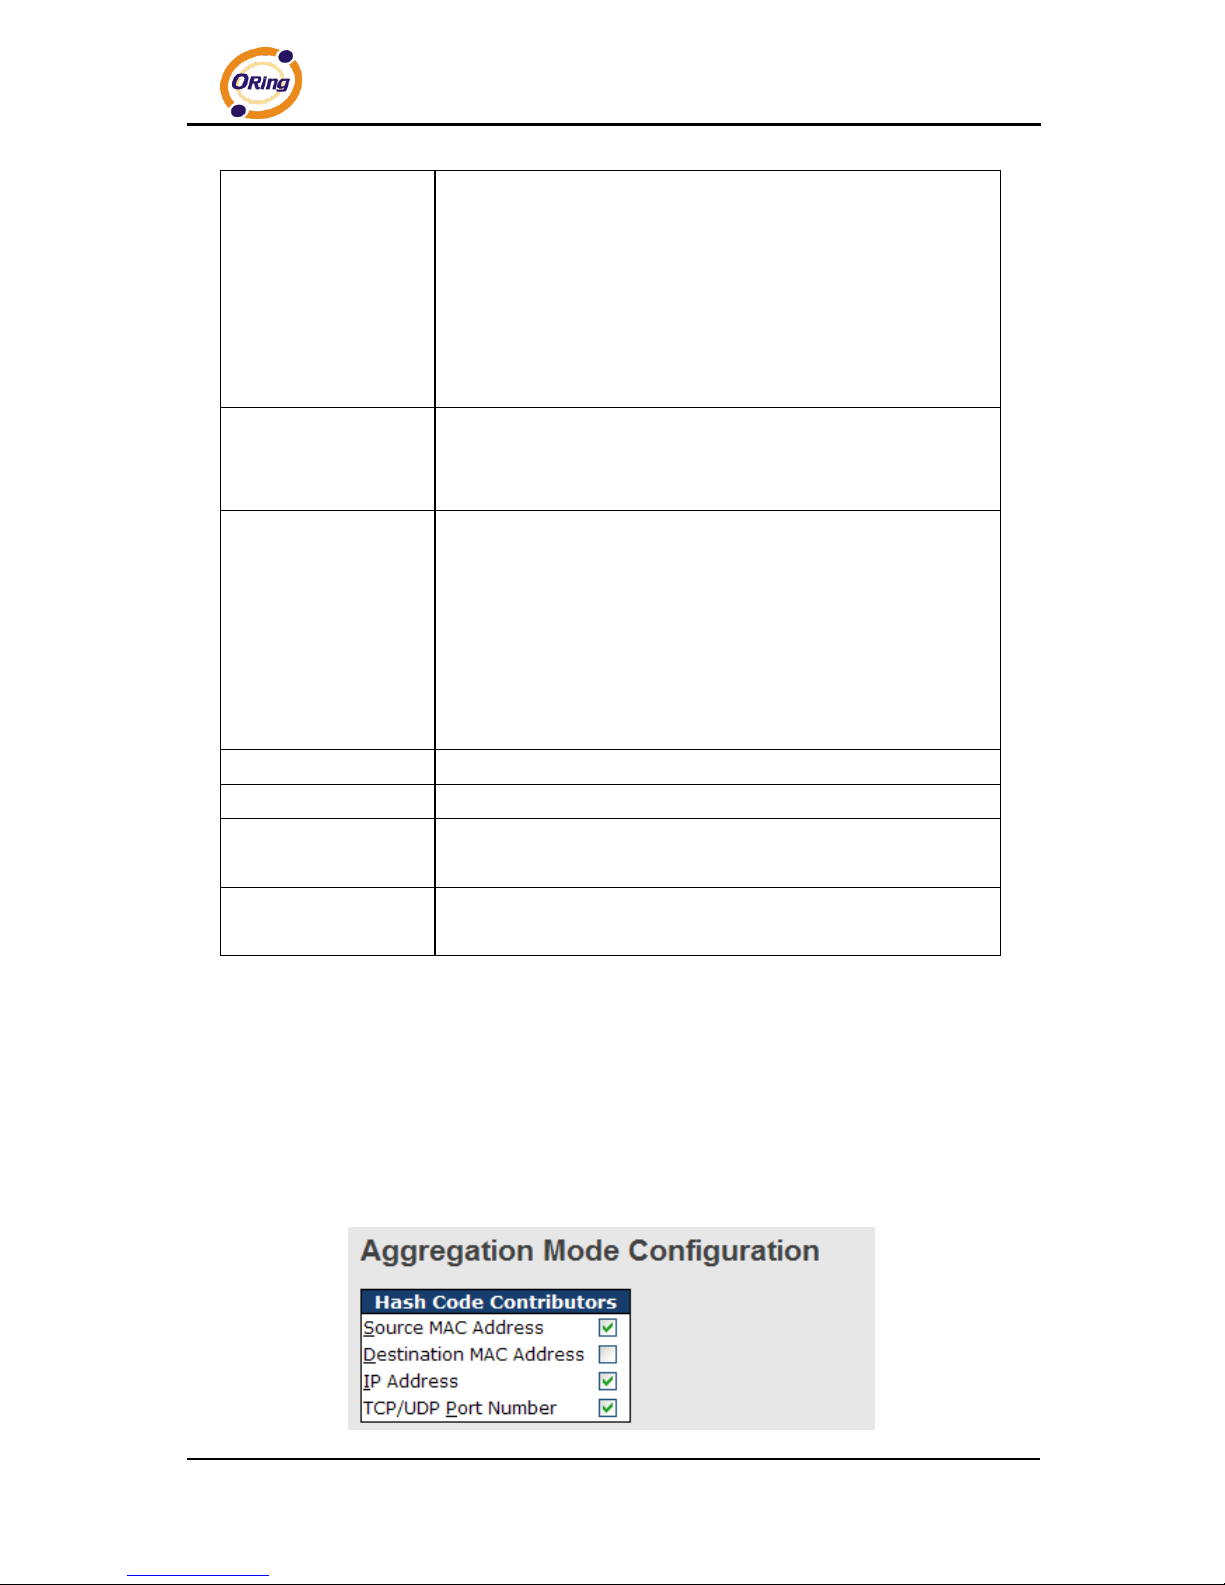
the aggregation hash mode and the aggregation group.
Page 52
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
51
Label
Description
Source MAC Address
Calculates the destination port of the frame. You can check this
box to enable the source MAC address, or uncheck to disable. By
default, Source MAC Address is enabled.
Destination MAC
Address
Calculates the destination port of the frame. You can check this
box to enable the destination MAC address, or uncheck to
disable. By default, Destination MAC Address is disabled.
IP Address
Calculates the destination port of the frame. You can check this
box to enable the IP address, or uncheck to disable. By default, IP
Address is enabled.
TCP/UDP Port
Number
Calculates the destination port of the frame. You can check this
box to enable the TCP/UDP port number, or uncheck to disable.
By default, TCP/UDP Port Number is enabled.
Label
Description
Group ID
Indicates the ID of each aggregation group. Normal means no
aggregation. Only one group ID is valid per port.
Port Members
Lists each switch port for each group ID. Select a radio button to
include a port in an aggregation, or clear the radio button to remove
the port from the aggregation. By default, no ports belong to any
aggregation group. Only full duplex ports can join an aggregation and
the ports must be in the same speed in each group.
Page 53
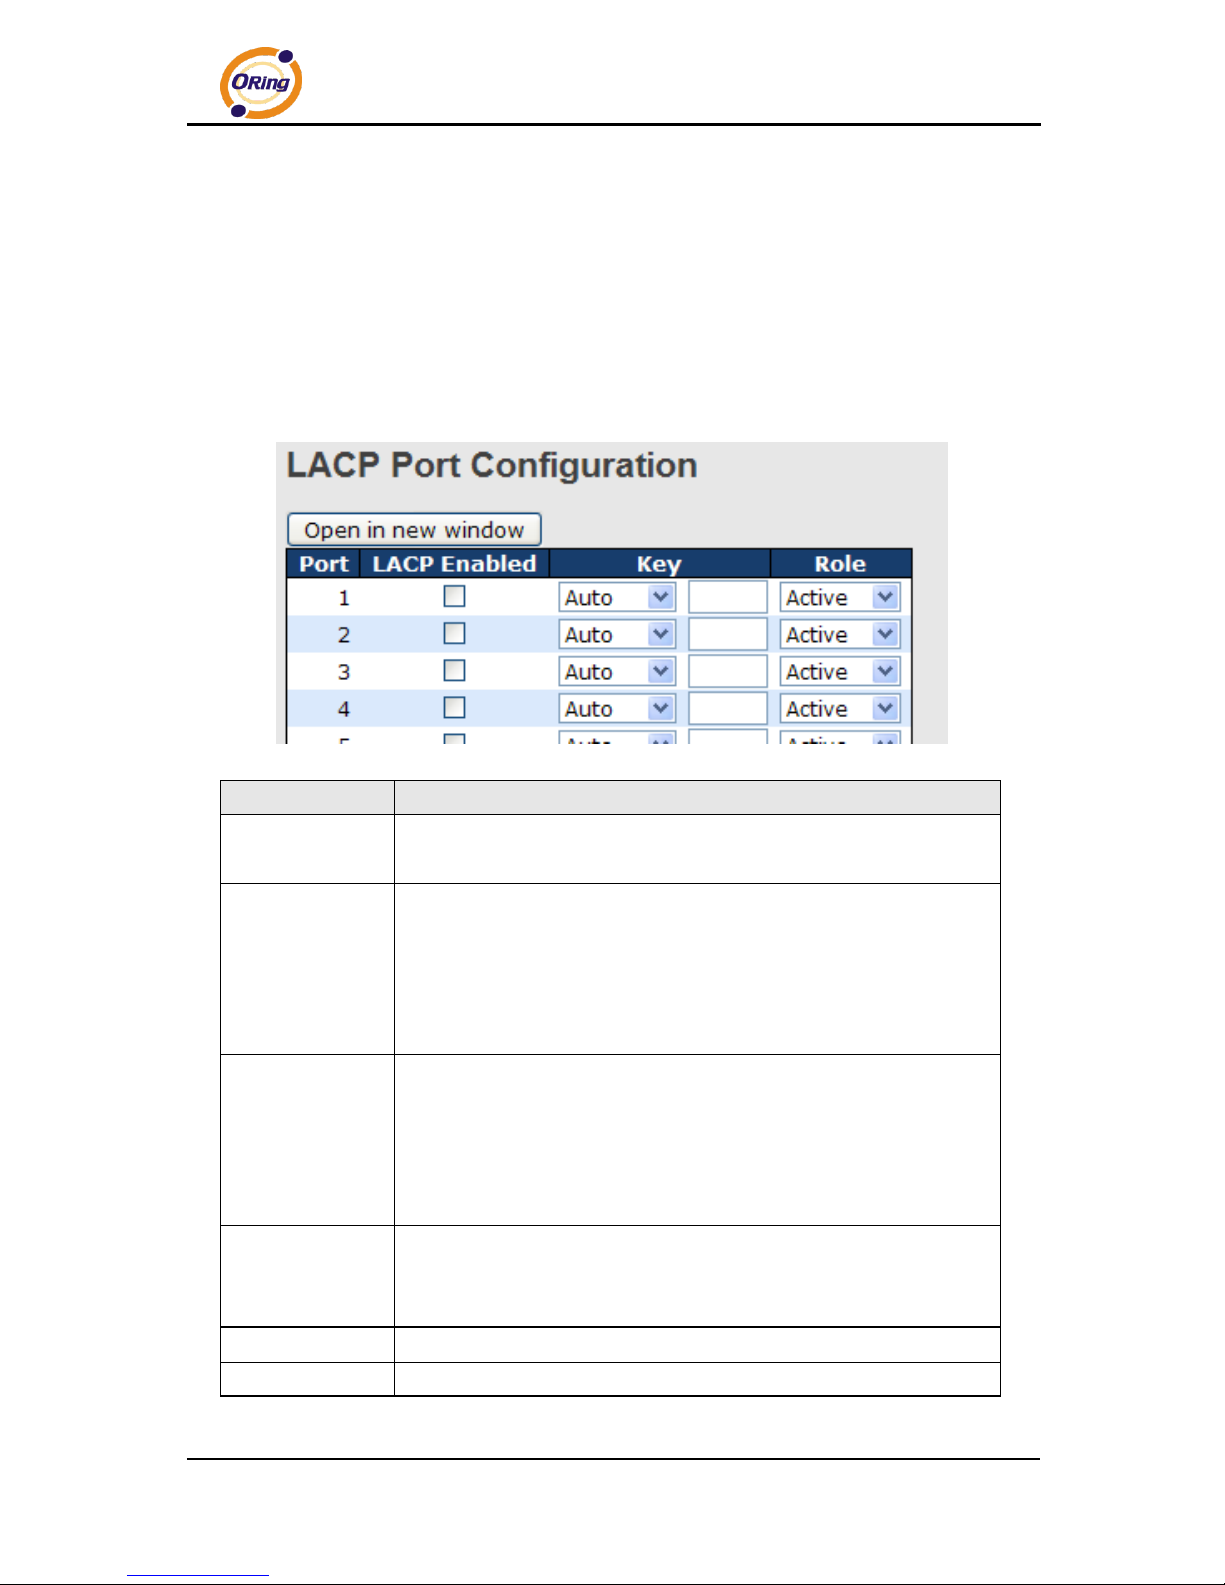
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
52
5.3.3 LACP
LACP (Link Aggregation Control Protocol) trunks are similar to static port trunks, but they are
more flexible because LACP is compliant with the IEEE 802.3ad standard. Hence, it is
interoperable with equipment from other vendors that also comply with the standard. This page
allows you to enable LACP functions to group ports together to form single virtual links and
change associated settings, thereby increasing the bandwidth between the switch and other
LACP-compatible devices.
Label
Description
Port
Indicates the ID of each aggregation group. Normal indicates there is
no aggregation. Only one group ID is valid per port.
LACP Enabled
Lists each switch port for each group ID. Check to include a port in an
aggregation, or clear the box to remove the port from the aggregation.
By default, no ports belong to any aggregation group. Only full duplex
ports can join an aggregation and the ports must be in the same speed
in each group.
Key
The Key value varies with the port, ranging from 1 to 65535. Auto will
set the key according to the physical link speed (10Mb = 1, 100Mb = 2,
1Gb = 3). Specific allows you to enter a user-defined value. Ports with
the same key value can join in the same aggregation group, while
ports with different keys cannot.
Role
Indicates LACP activity status. Active will transmit LACP packets
every second, while Passive will wait for a LACP packet from a partner
(speak if spoken to).
Save
Click to save changes
Reset
Click to undo changes made locally and revert to previous values
Page 54
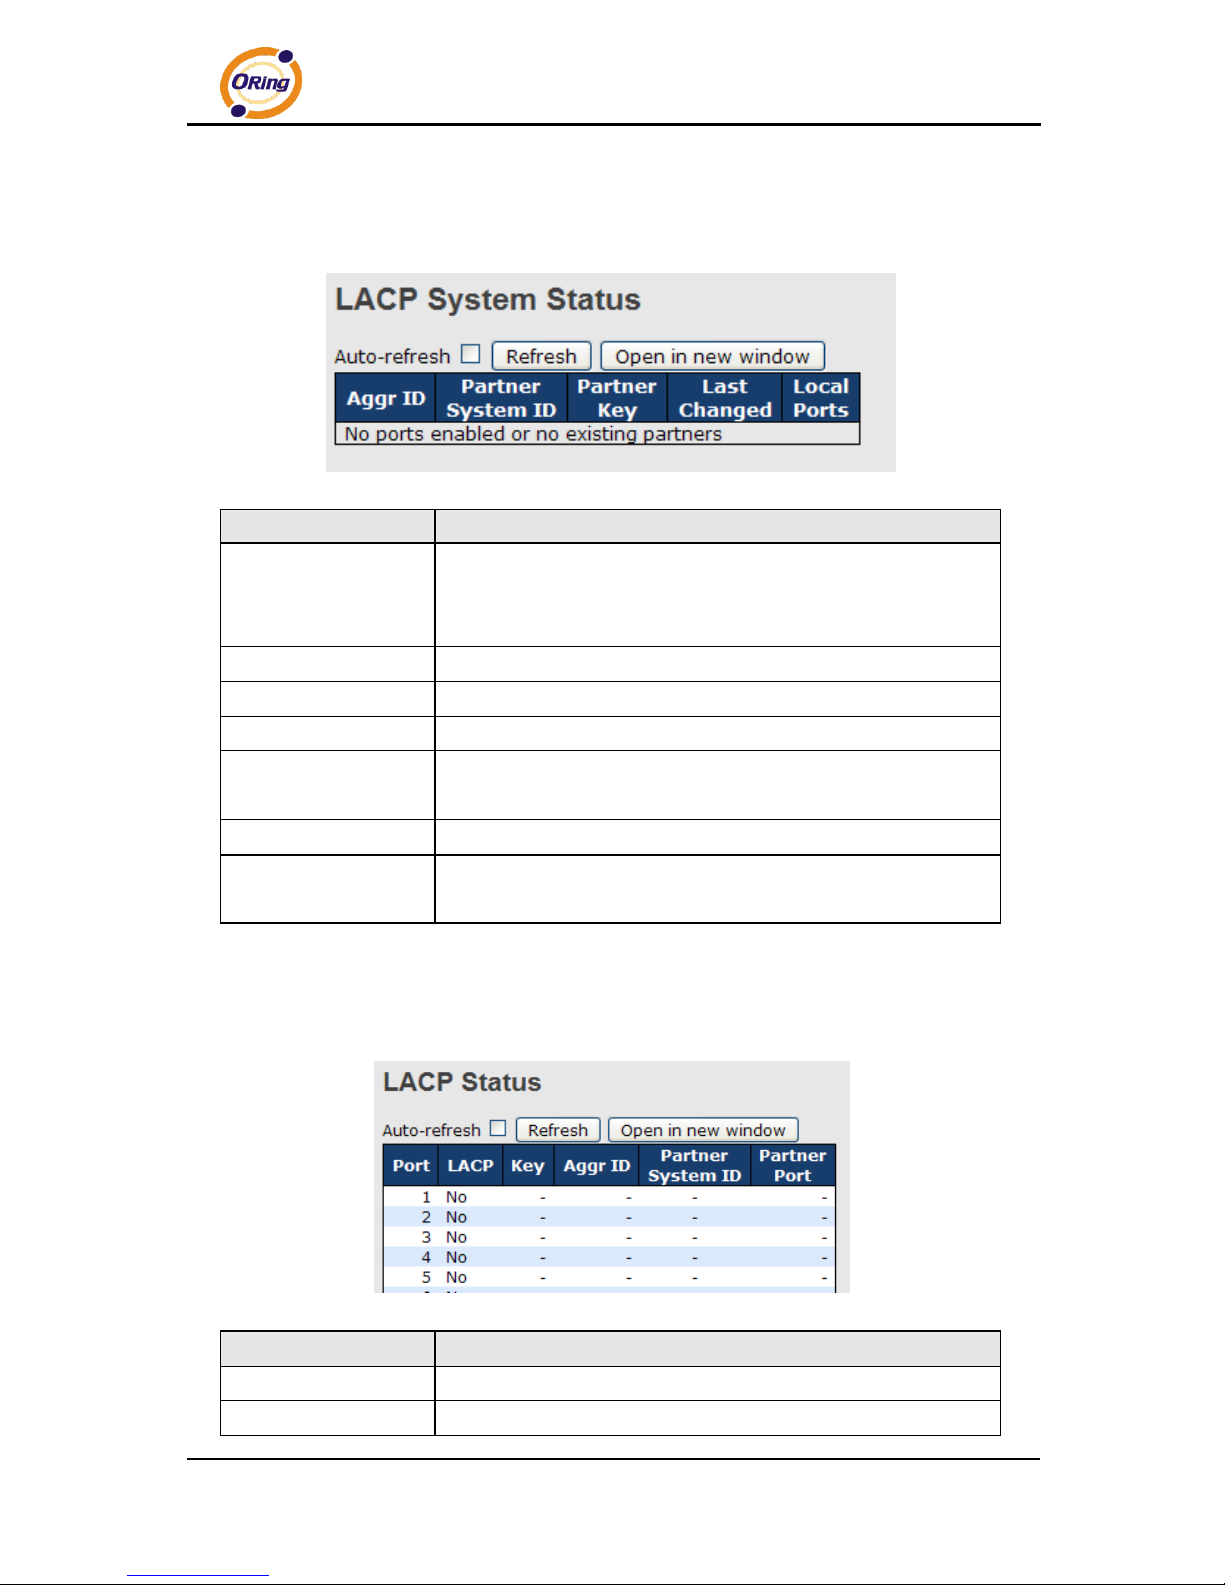
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
53
LACP System Status
This page provides a status overview for all LACP instances.
Label
Description
Aggr ID
The aggregation ID is associated with the aggregation instance.
For LLAG, the ID is shown as 'isid:aggr-id' and for GLAGs as
'aggr-id'
Partner System ID
System ID (MAC address) of the aggregation partner
Partner Key
The key assigned by the partner to the aggregation ID
Last Changed
The time since this aggregation changed.
Local Ports
Indicates which ports belong to the aggregation of the
switch/stack. The format is: "Switch ID:Port".
Refresh
Click to refresh the page immediately
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
LACP Status
This page provides an overview of the LACP status for all ports.
Label
Description
Port
Switch port number
LACP
Yes means LACP is enabled and the port link is up. No means
Page 55
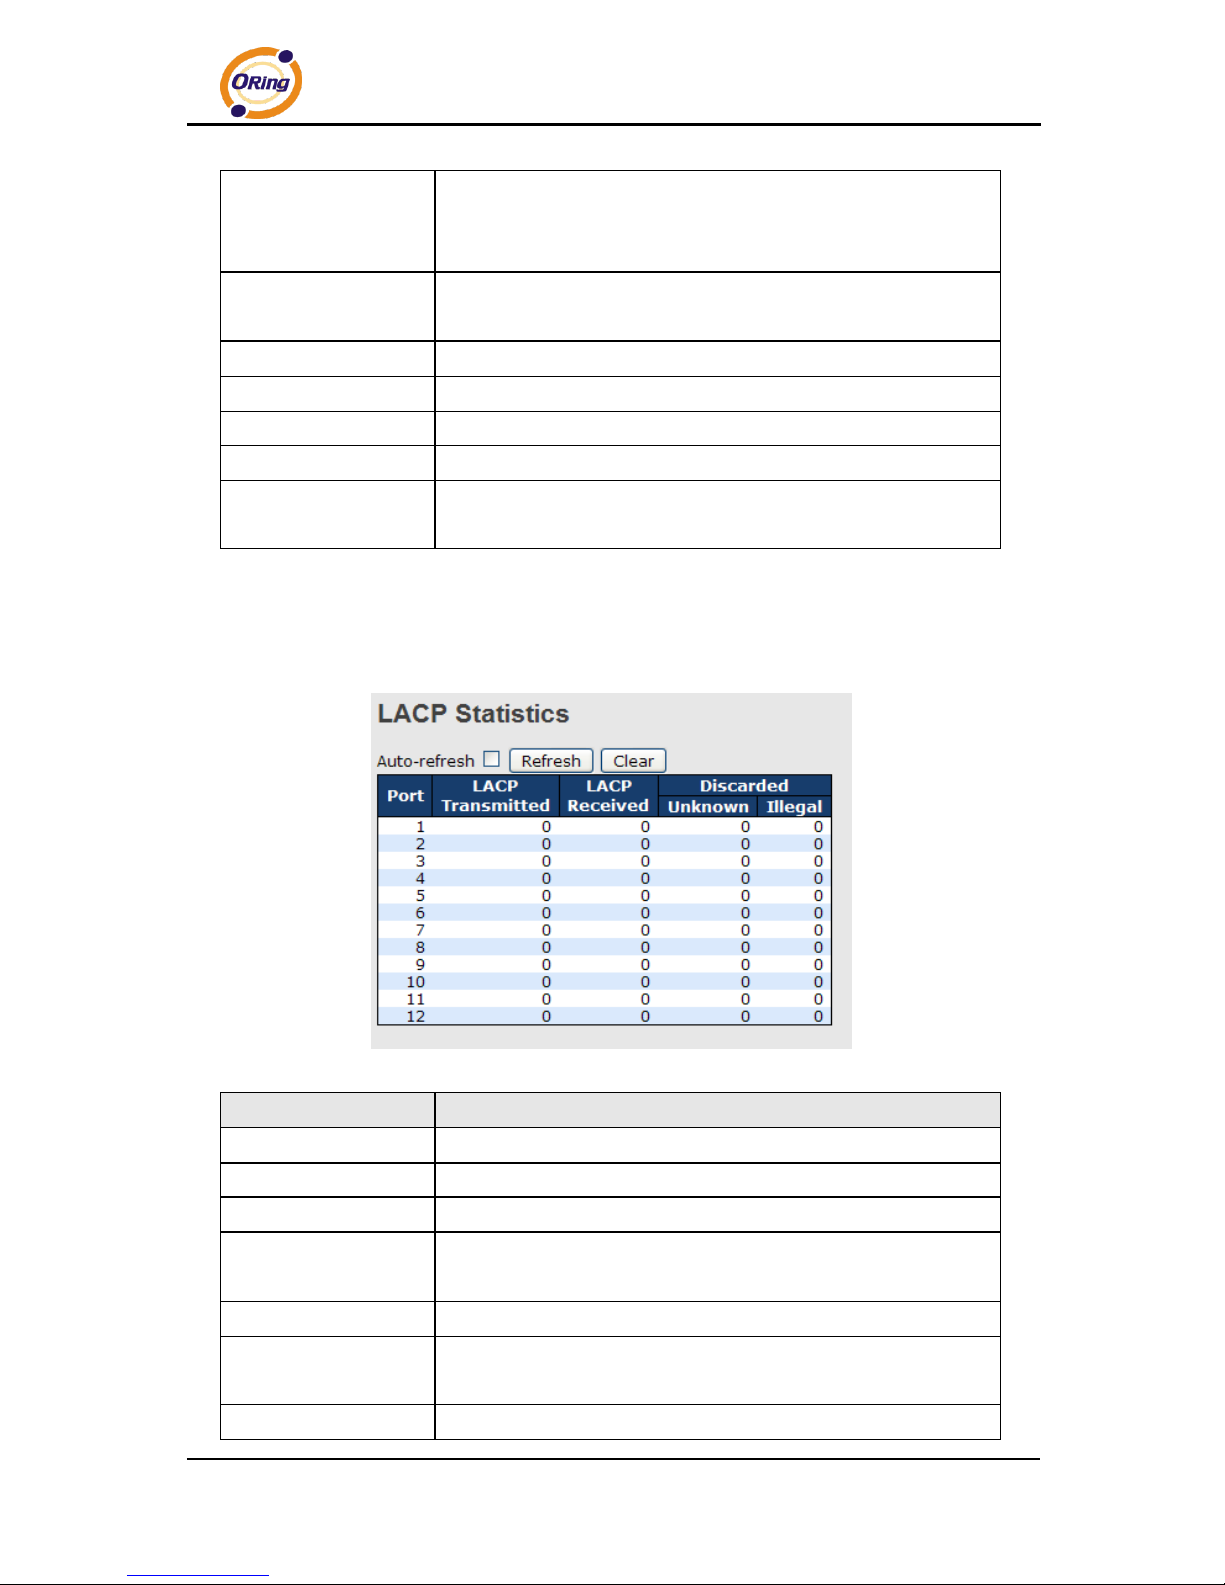
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
54
LACP is not enabled or the port link is down. Backup means the
port cannot join in the aggregation group unless other ports are
removed. The LACP status is disabled.
Key
The key assigned to the port. Only ports with the same key can be
aggregated
Aggr ID
The aggregation ID assigned to the aggregation group
Partner System ID
The partner‟s system ID (MAC address)
Partner Port
The partner‟s port number associated with the port
Refresh
Click to refresh the page immediately
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
LACP Statistics
This page provides an overview of the LACP statistics for all ports.
Label
Description
Port
Switch port number
LACP Transmitted
The number of LACP frames sent from each port
LACP Received
The number of LACP frames received at each port
Discarded
The number of unknown or illegal LACP frames discarded at each
port.
Refresh
Click to refresh the page immediately
Auto-refresh
Check to enable an automatic refresh of the page at regular
intervals
Clear
Click to clear the counters for all ports
Page 56
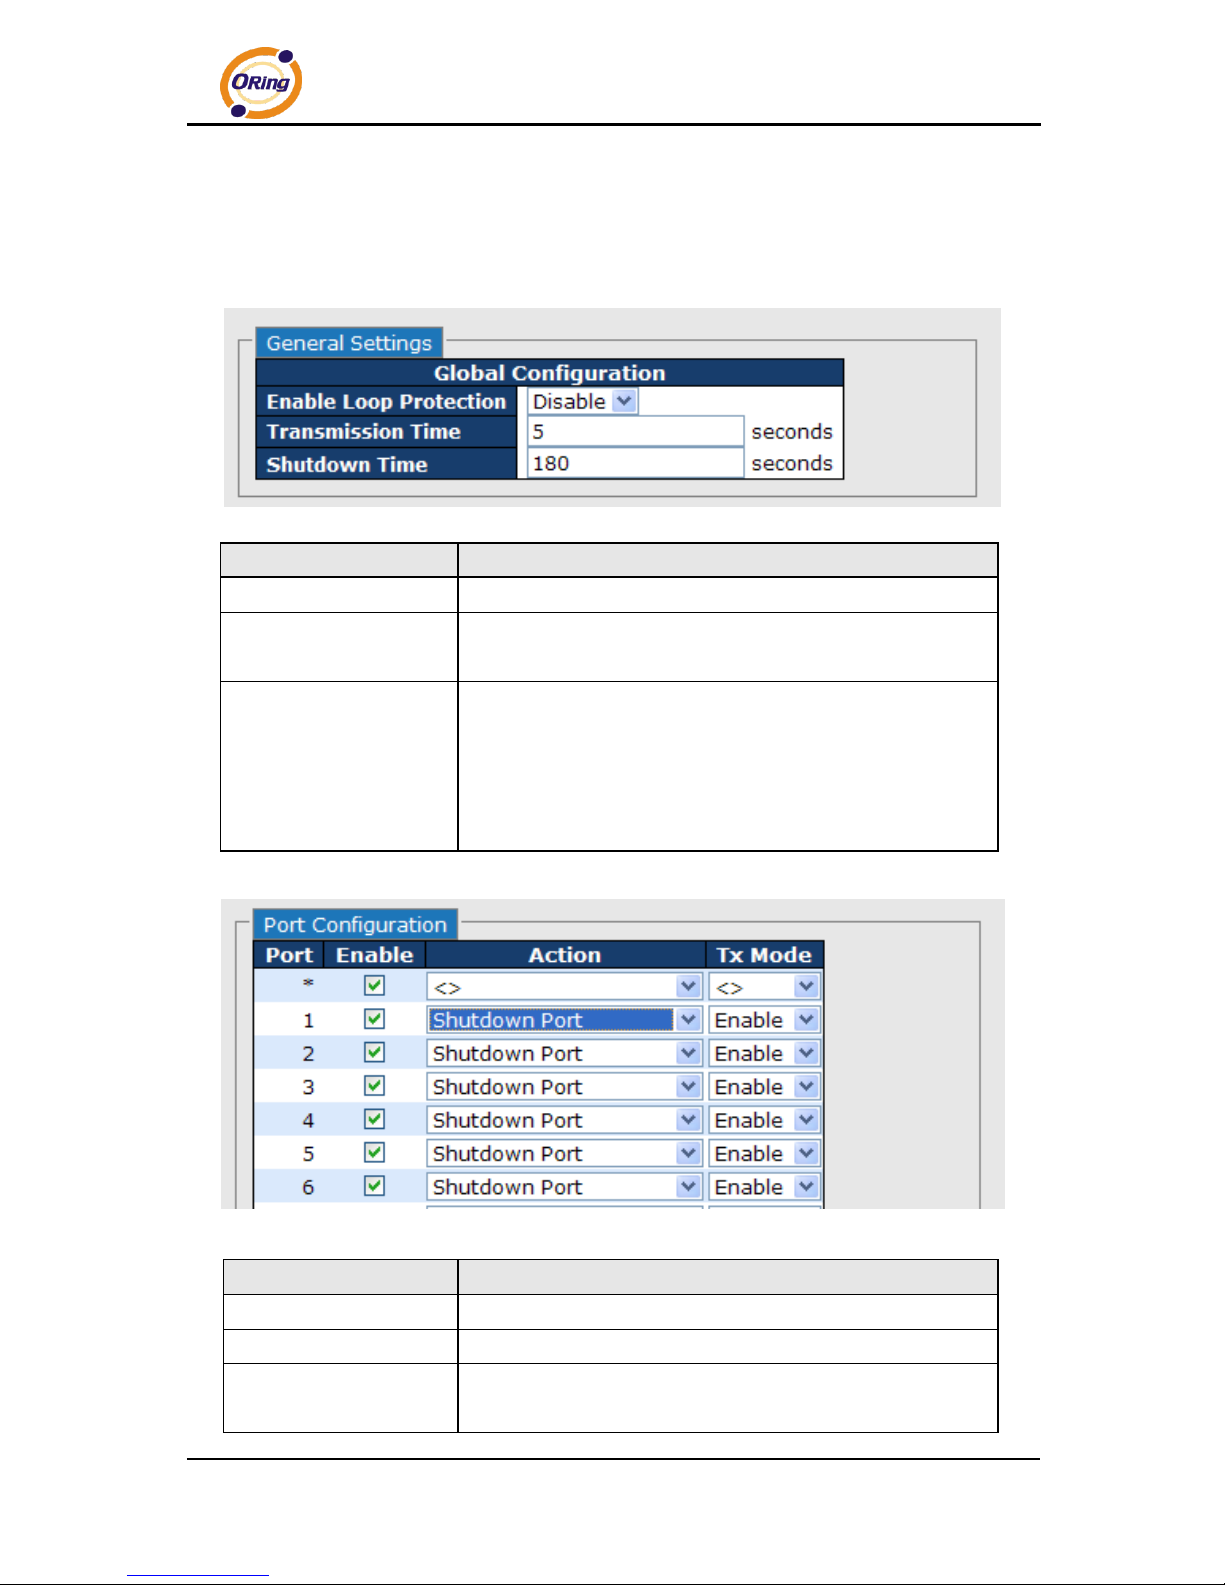
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
55
5.3.4 Loop Gourd
This feature prevents loop attack. When receiving loop packets, the port will be disabled
automatically, preventing the loop attack from affecting other network devices.
Label
Description
Enable Loop Protection
Activate loop protection functions (as a whole)
Transmission Time
The interval between each loop protection PDU sent on each
port. The valid value is 1 to 10 seconds.
Shutdown Time
The period (in seconds) for which a port will be kept disabled
when a loop is detected (shutting down the port). The valid
value is 0 to 604800 seconds (7 days). A value of zero will
keep a port disabled permanently (until the device is
restarted).
Label
Description
Port
Switch port number
Enable
Activate loop protection functions (as a whole)
Action
Configures the action to take when a loop is detected. Valid
values include Shutdown Port, Shutdown Port, and Log or
Page 57
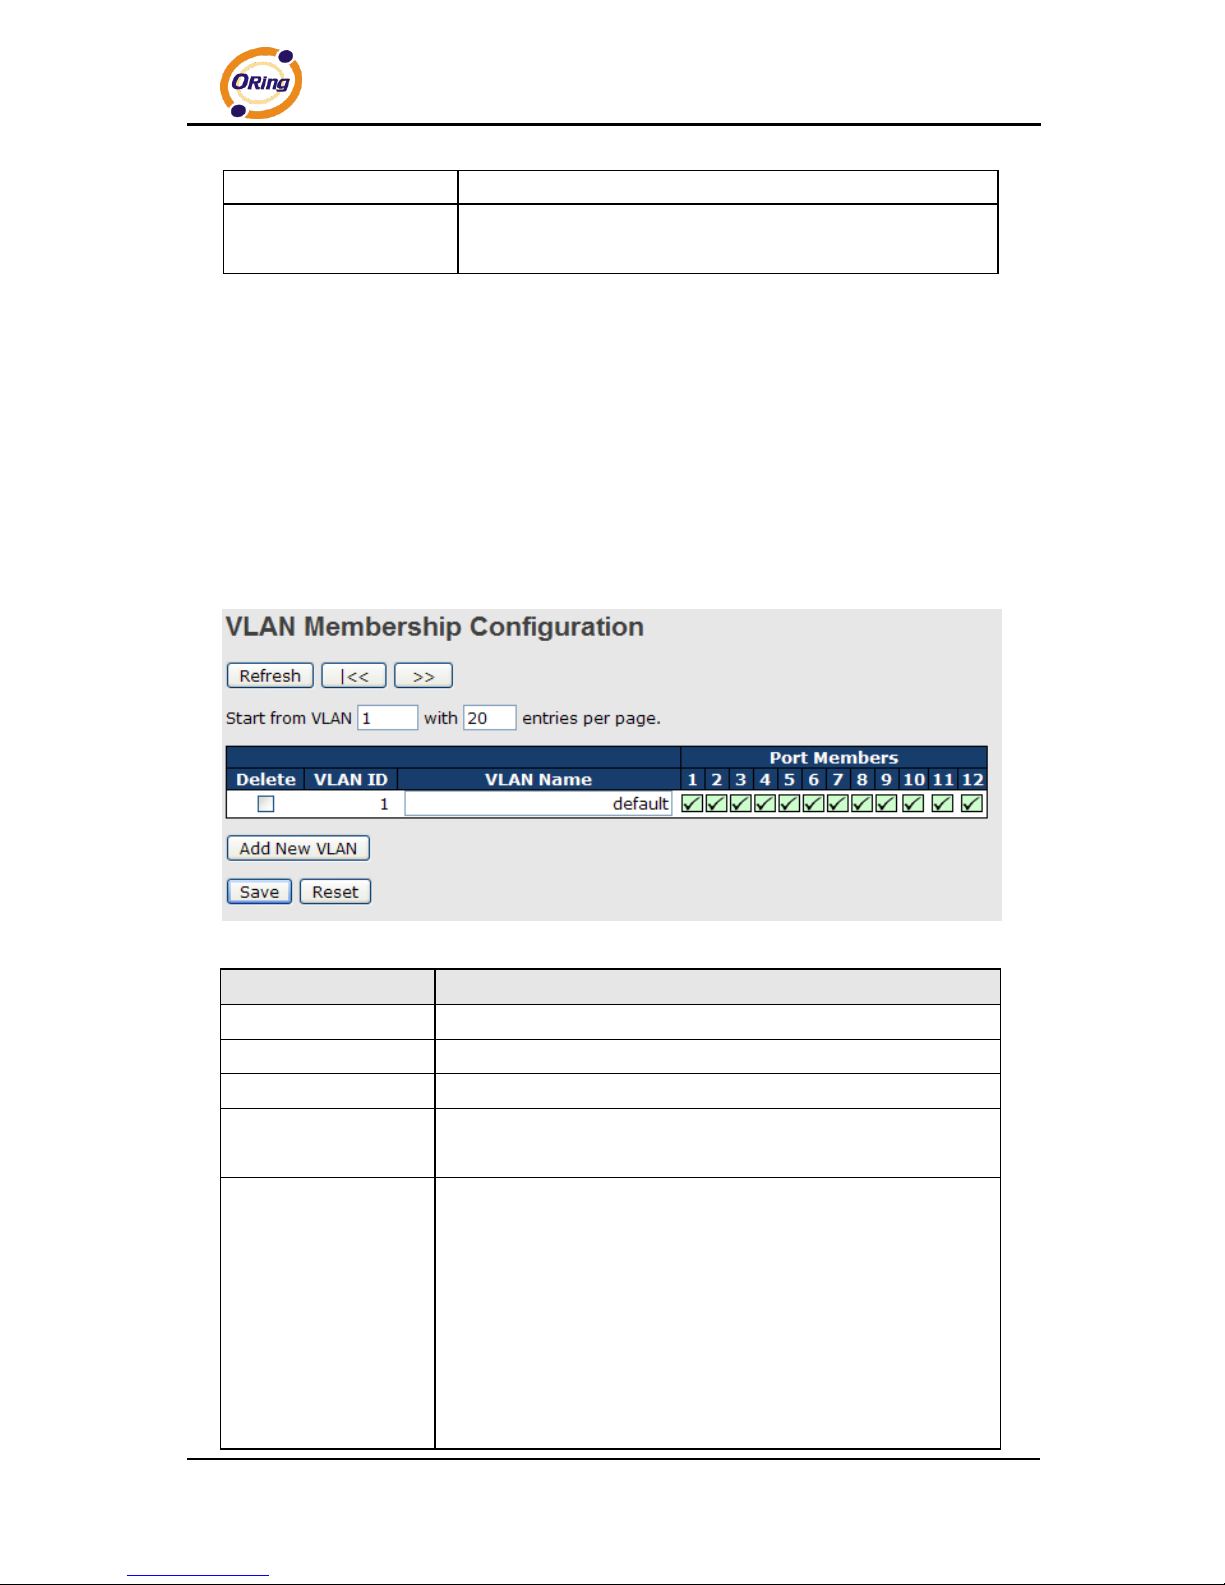
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
56
Log Only.
Tx Mode
Controls whether the port is actively generating loop protection
PDUs or only passively look for looped PDUs.
5.4 VLAN
5.4.1 VLAN Membership
A VLAN (Virtual LAN) is a logical LAN based on a physical LAN with links that does not consist
of a physical (wired or wireless) connection between two computing devices but is
implemented using methods of network virtualization. A VLAN can be created by partitioning a
physical LAN into multiple logical LANs using a VLAN ID. You can assign switch ports to a
VLAN and add new VLANs in this page.
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
VLAN ID
The VLAN ID for the entry
MAC Address
The MAC address for the entry
Port Members
Checkmarks indicate which ports are members of the entry.
Check or uncheck as needed to modify the entry
Add New VLAN
Click to add a new VLAN ID. An empty row is added to the table,
and the VLAN can be configured as needed. Valid values for a
VLAN ID are 1 through 4095.
After clicking Save, the new VLAN will be enabled on the selected
switch stack but contains no port members.
A VLAN without any port members on any stack will be deleted
when you click Save.
Click Delete to undo the addition of new VLANs.
Page 58
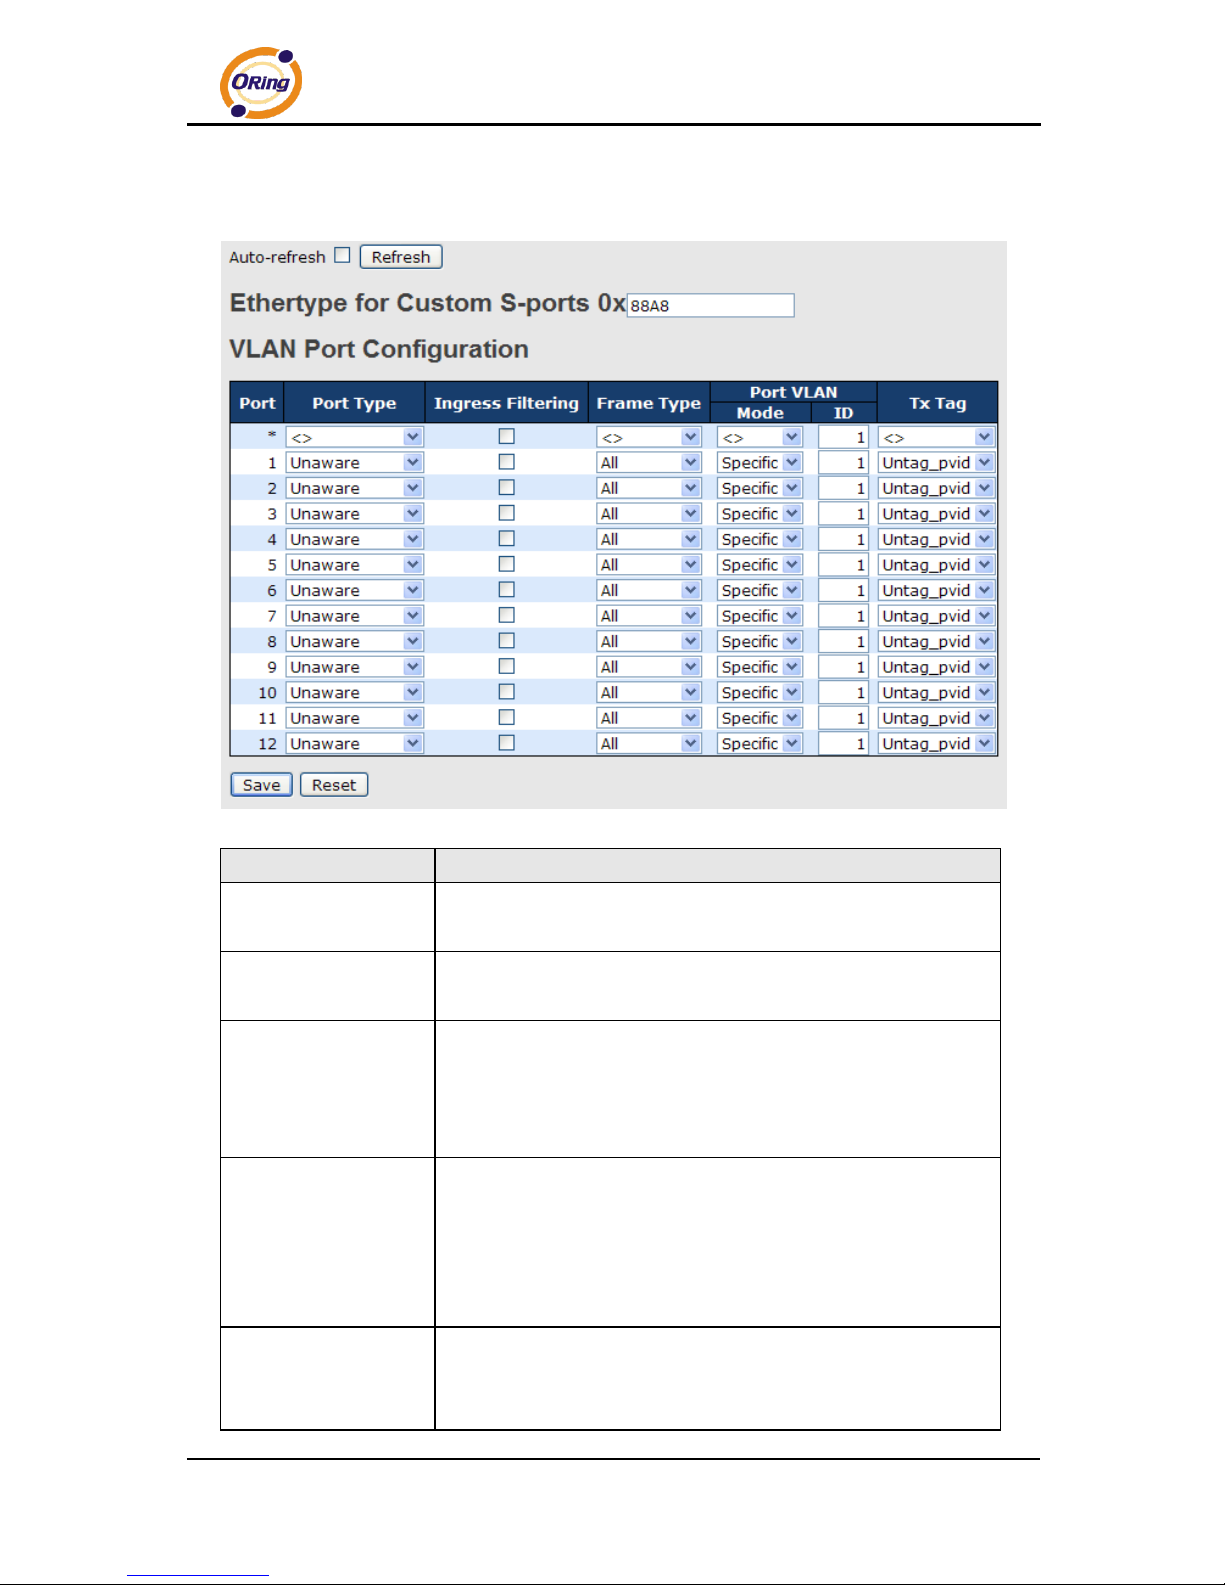
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
57
5.4.2 Port Configurations
This page allows you to set up VLAN ports individually.
Label
Description
Ethertype for
customer S-Ports
This field specifies the Ether type used for custom S-ports. This is
a global setting for all custom S-ports.
Port
The switch port number to which the following settings will be
applied.
Port type
Port can be one of the following types: Unaware, Customer
(C-port), Service (S-port), Custom Service (S-custom-port).
If port type is Unaware, all frames are classified to the port VLAN
ID and tags are not removed.
Ingress Filtering
Enable ingress filtering on a port by checking the box. This
parameter affects VLAN ingress processing. If ingress filtering is
enabled and the ingress port is not a member of the classified
VLAN of the frame, the frame will be discarded. By default,
ingress filtering is disabled (no check mark).
Frame Type
Determines whether the port accepts all frames or only
tagged/untagged frames. This parameter affects VLAN ingress
processing. If the port only accepts tagged frames, untagged
Page 59
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
58
frames received on the port will be discarded. By default, the field
is set to All.
Port VLAN Mode
The allowed values are None or Specific. This parameter affects
VLAN ingress and egress processing.
If None is selected, a VLAN tag with the classified VLAN ID is
inserted in frames transmitted on the port. This mode is normally
used for ports connected to VLAN-aware switches. Tx tag should
be set to Untag_pvid when this mode is used.
If Specific (the default value) is selected, a port VLAN ID can be
configured (see below). Untagged frames received on the port are
classified to the port VLAN ID. If VLAN awareness is disabled, all
frames received on the port are classified to the port VLAN ID. If
the classified VLAN ID of a frame transmitted on the port is
different from the port VLAN ID, a VLAN tag with the classified
VLAN ID will be inserted in the frame.
Port VLAN ID
Configures the VLAN identifier for the port. The allowed range of
the values is 1 through 4095. The default value is 1.
Note: The port must be a member of the same VLAN as the port
VLAN ID.
Tx Tag
Determines egress tagging of a port. Untag_pvid: all VLANs
except the configured PVID will be tagged. Tag_all: all VLANs are
tagged. Untag_all: all VLANs are untagged.
Introduction of Port Types
Below is a detailed description of each port type, including Unaware, C-port, S-port, and
S-custom-port.
Ingress action
Egress action
Unaware
The function of
Unaware can
be used for
802.1QinQ
(double tag).
When the port receives untagged frames, an
untagged frame obtains a tag (based on PVID)
and is forwarded.
When the port receives tagged frames:
1. If the tagged frame contains a TPID of
0x8100, it will become a double-tag frame and
will be forwarded.
2. If the TPID of tagged frame is not 0x8100
(ex. 0x88A8), it will be discarded.
The TPID of a frame
transmitted by Unaware
port will be set to
0x8100.
The final status of the
frame after egressing
will also be affected by
the Egress Rule.
C-port
When the port receives untagged frames, an
The TPID of a frame
Page 60
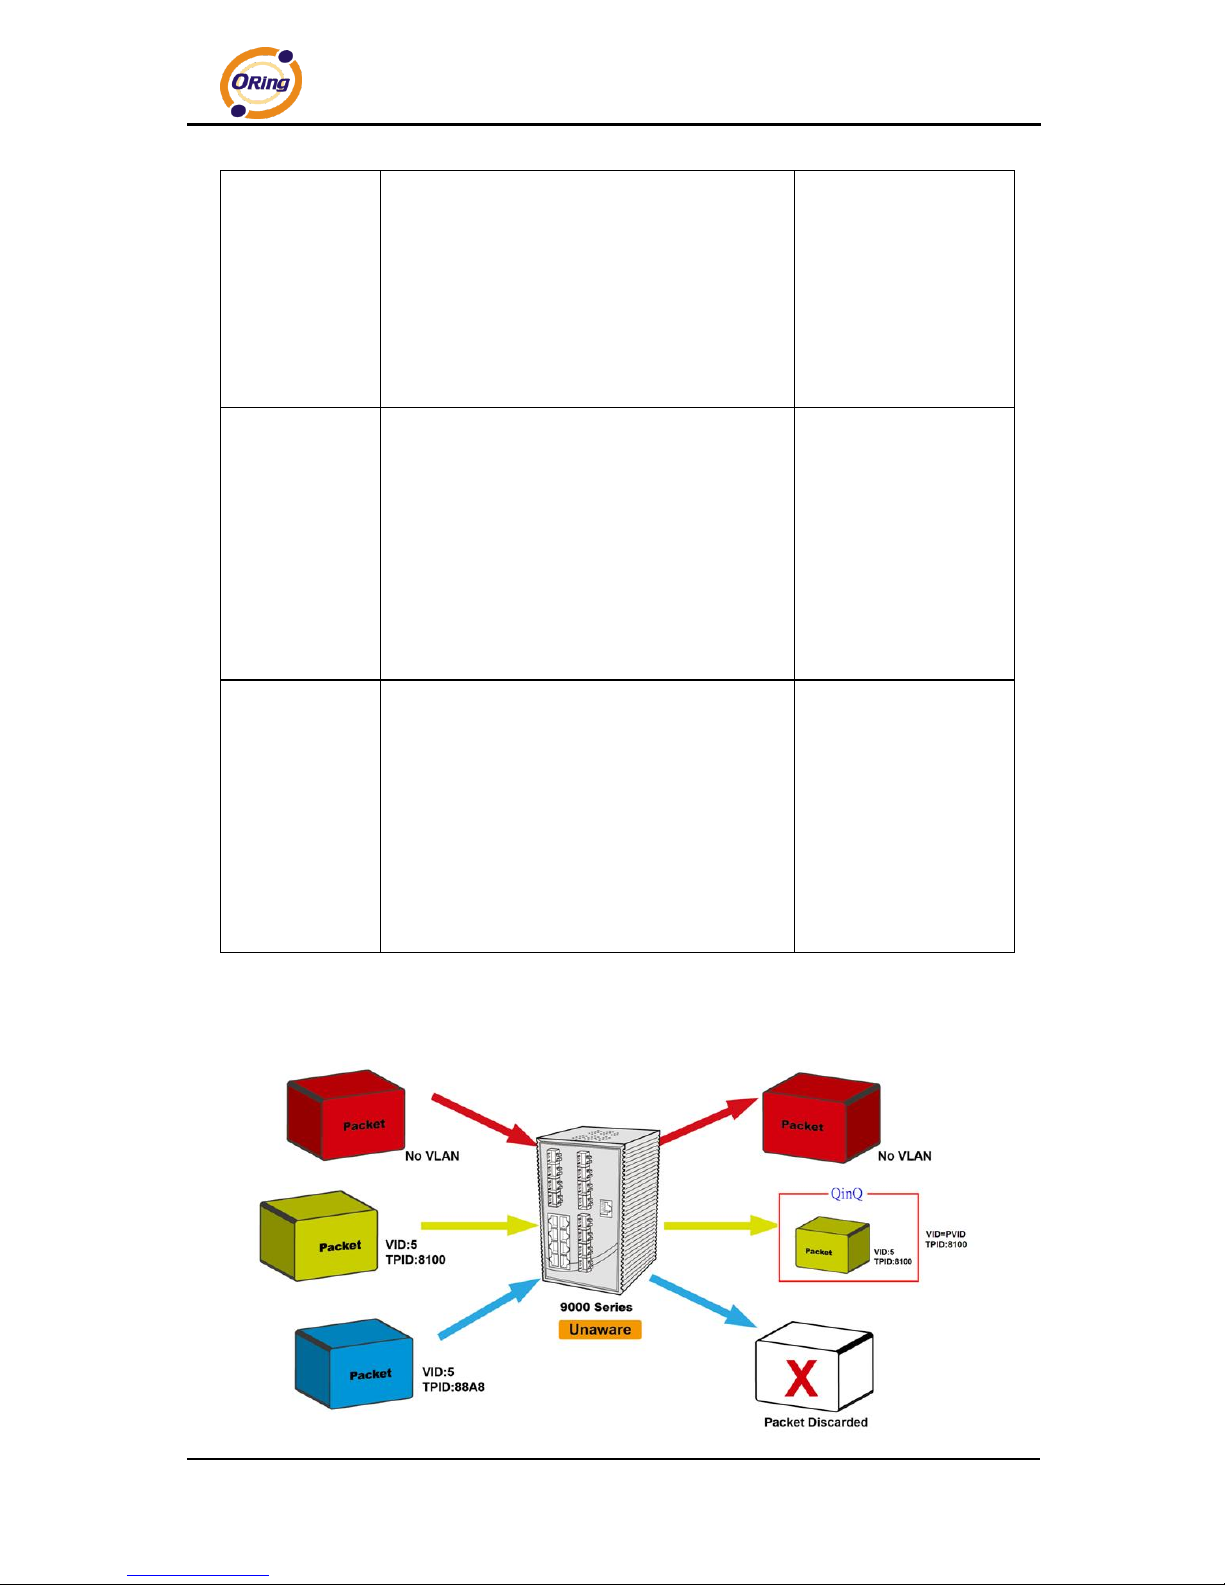
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
59
untagged frame obtains a tag (based on PVID)
and is forwarded.
When the port receives tagged frames:
1. If the tagged frame contains a TPID of
0x8100, it will be forwarded.
2. If the TPID of tagged frame is not 0x8100
(ex. 0x88A8), it will be discarded.
transmitted by C-port
will be set to 0x8100.
S-port
When the port receives untagged frames, an
untagged frame obtains a tag (based on PVID)
and is forwarded.
When the port receives tagged frames:
1. If the tagged frame contains a TPID of
0x8100, it will be forwarded.
2. If the TPID of tagged frame is not 0x88A8
(ex. 0x8100), it will be discarded.
The TPID of a frame
transmitted by S-port
will be set to 0x88A8.
S-custom-port
When the port receives untagged frames, an
untagged frame obtains a tag (based on PVID)
and is forwarded.
When the port receives tagged frames:
1. If the tagged frame contains a TPID of
0x8100, it will be forwarded.
2. If the TPID of tagged frame is not 0x88A8
(ex. 0x8100), it will be discarded.
The TPID of a frame
transmitted by
S-custom-port will be
set to a self-customized
value, which can be set
by the user via
Ethertype for Custom
S-ports.
Below are the illustrations of different port types:
Page 61
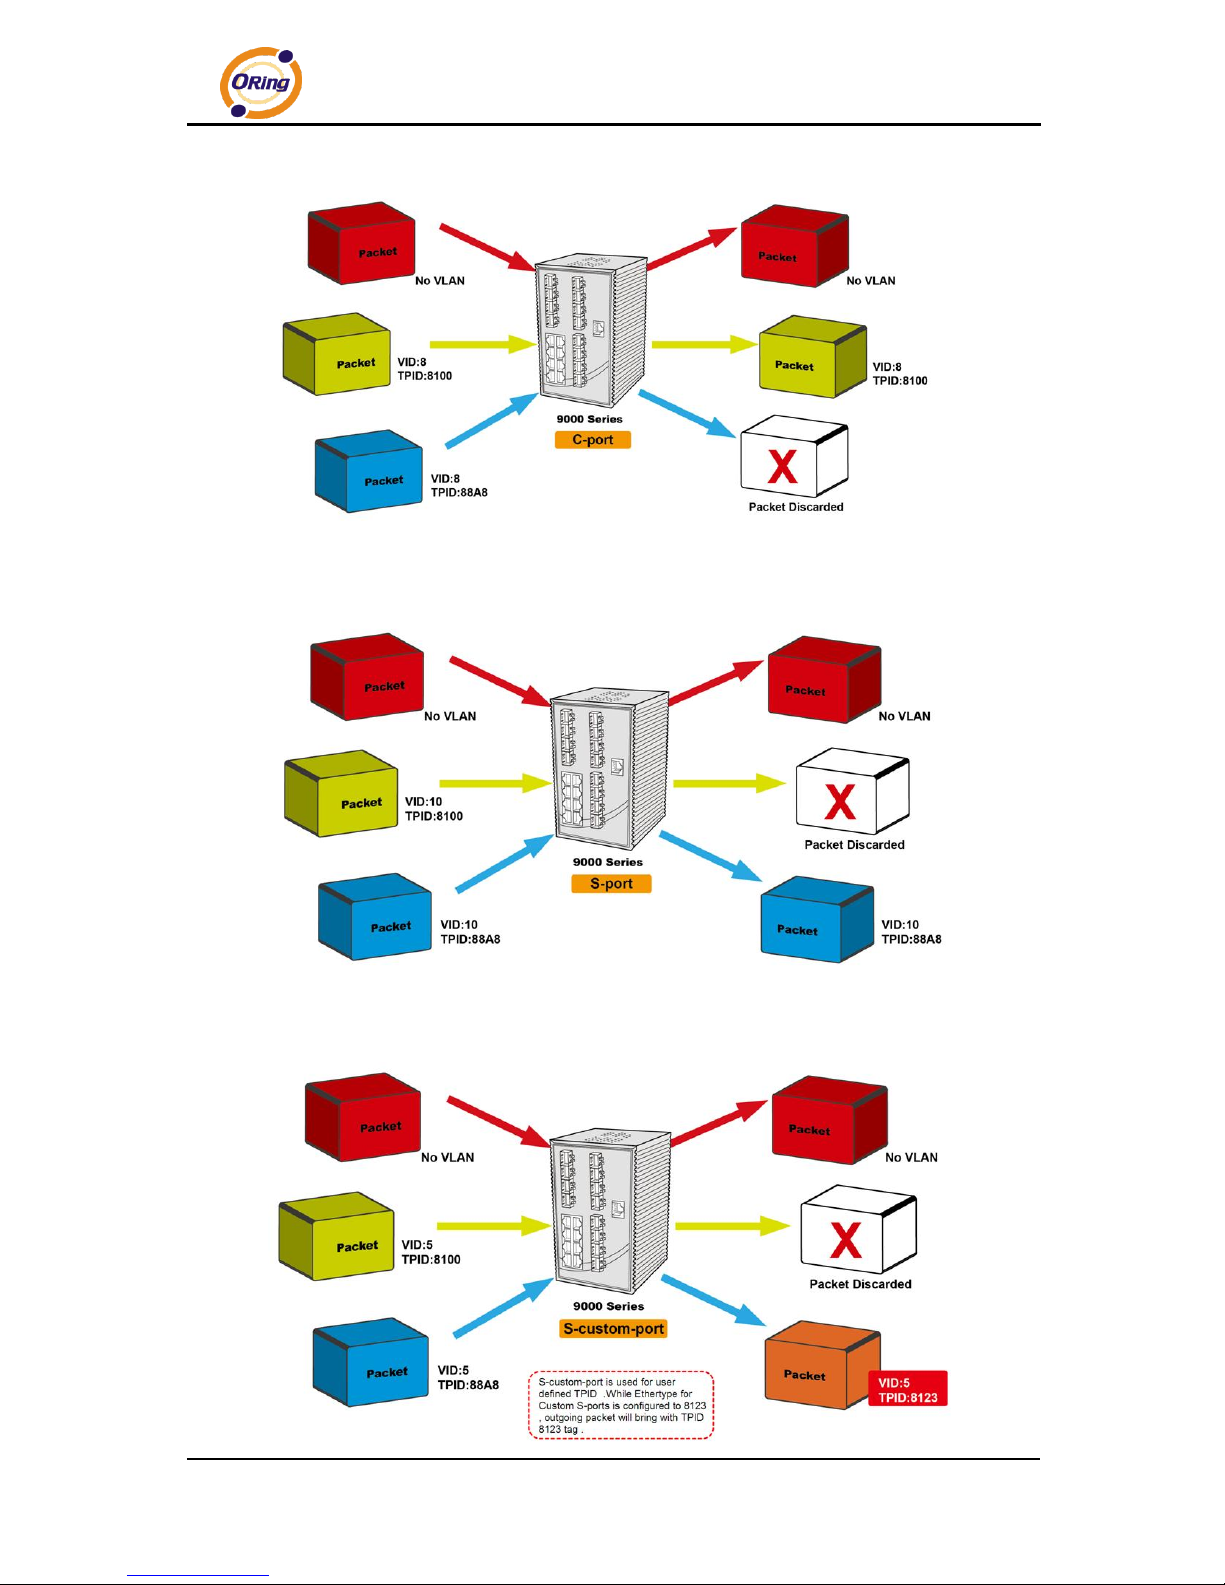
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
60
Page 62
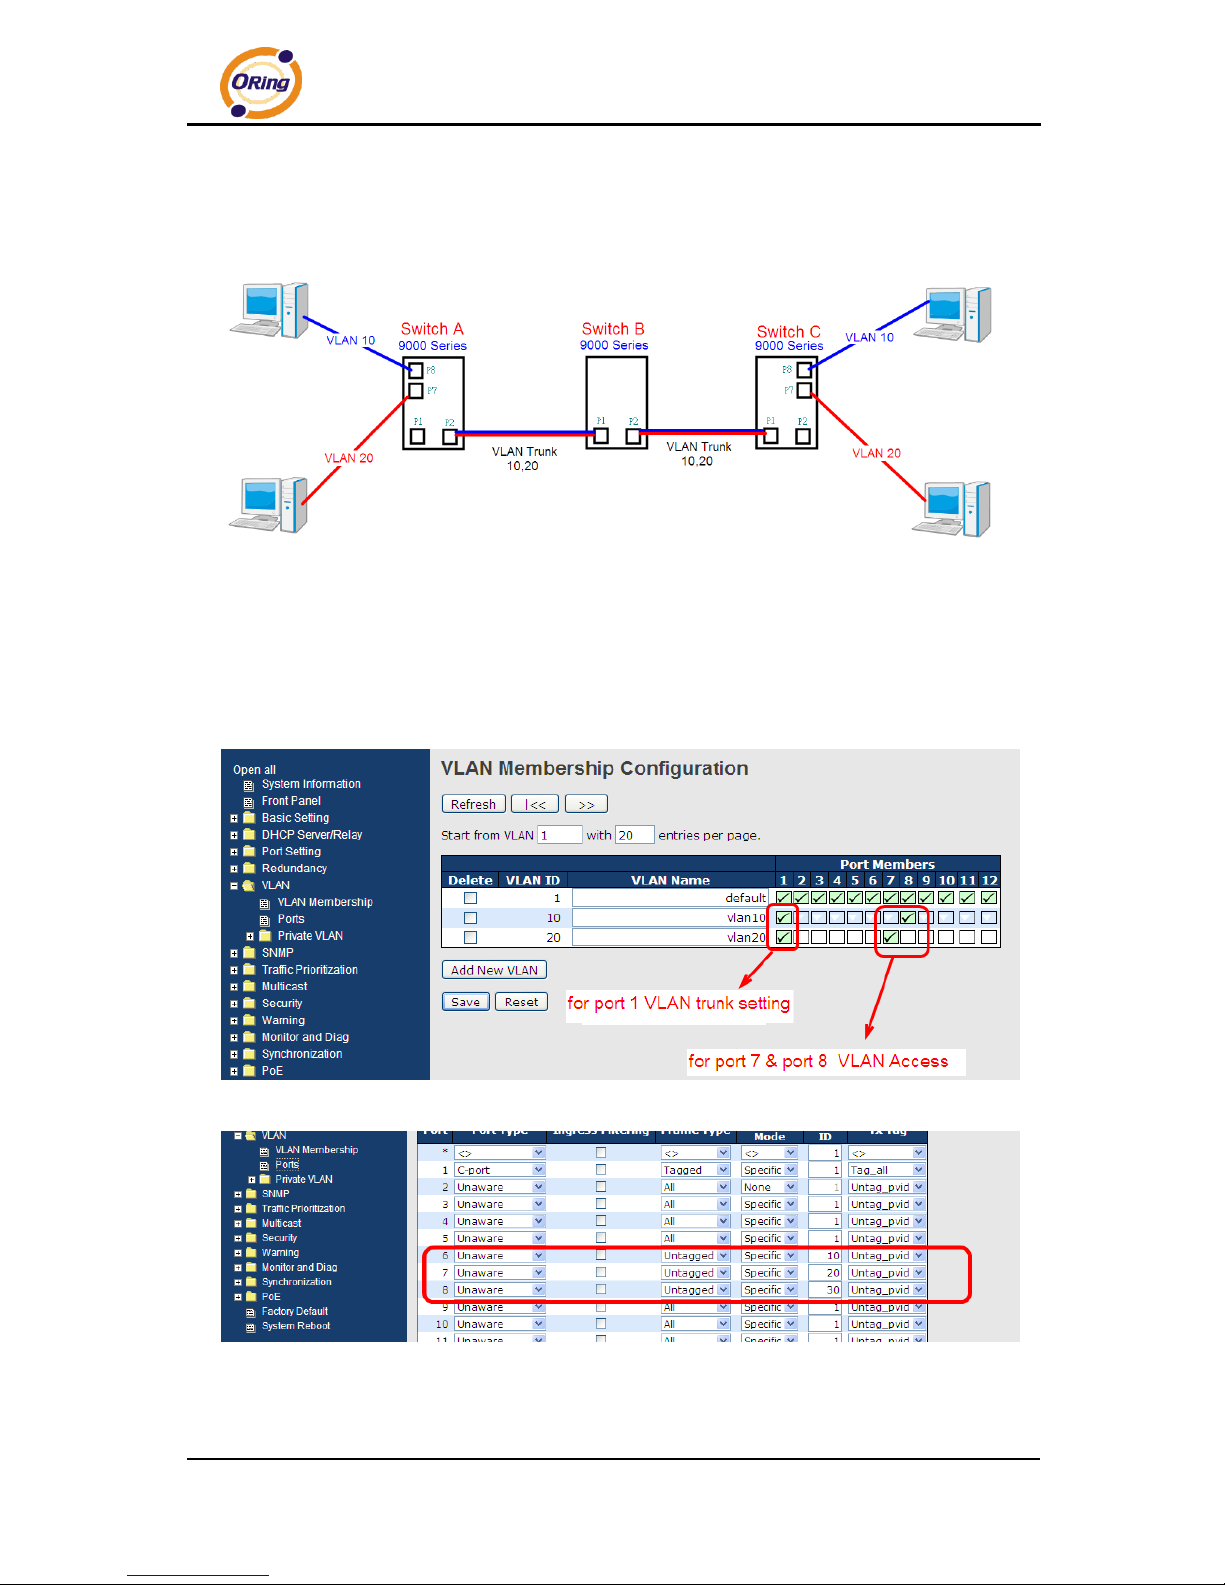
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
61
Examples of VLAN Settings
VLAN Access Mode:
Switch A,
Port 7 is VLAN Access mode = Untagged 20
Port 8 is VLAN Access mode = Untagged 10
Below are the switch settings.
Page 63
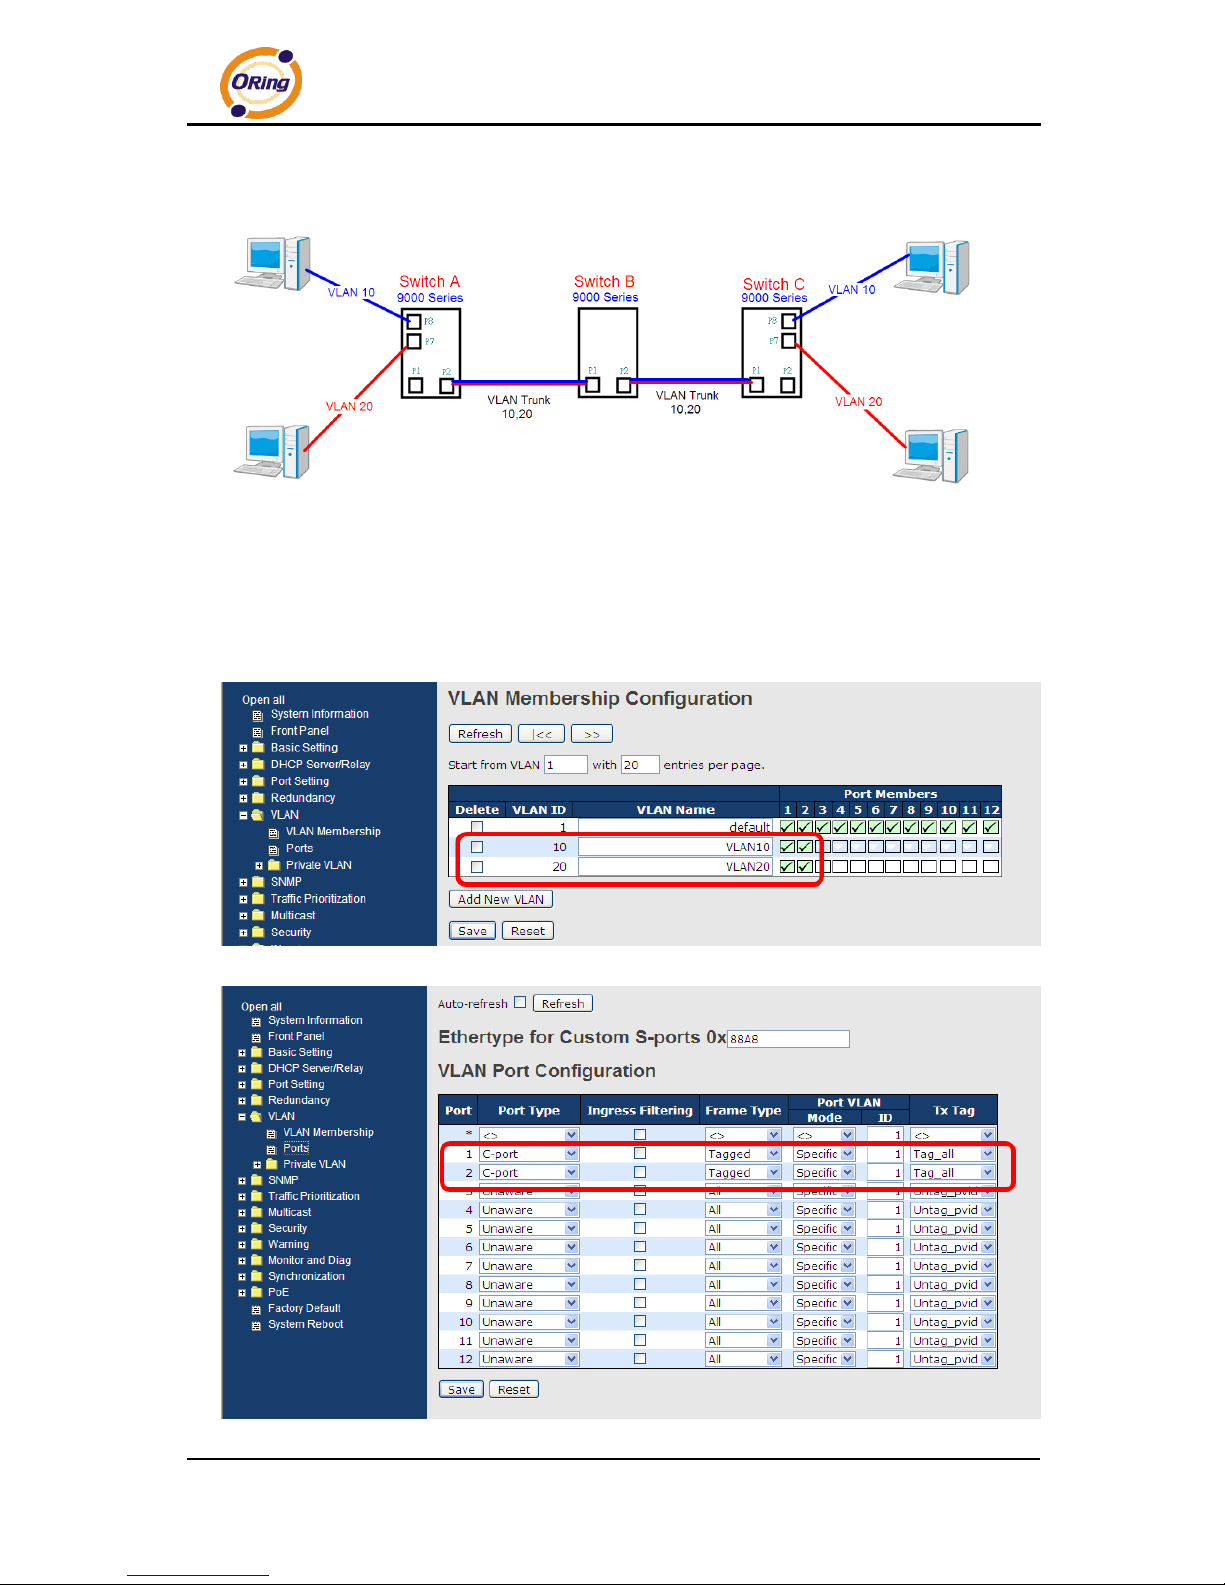
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
62
VLAN 1Q Trunk Mode:
Switch B,
Port 1 = VLAN 1Qtrunk mode = tagged 10, 20
Port 2 = VLAN 1Qtrunk mode = tagged 10, 20
Below are the switch settings.
Page 64
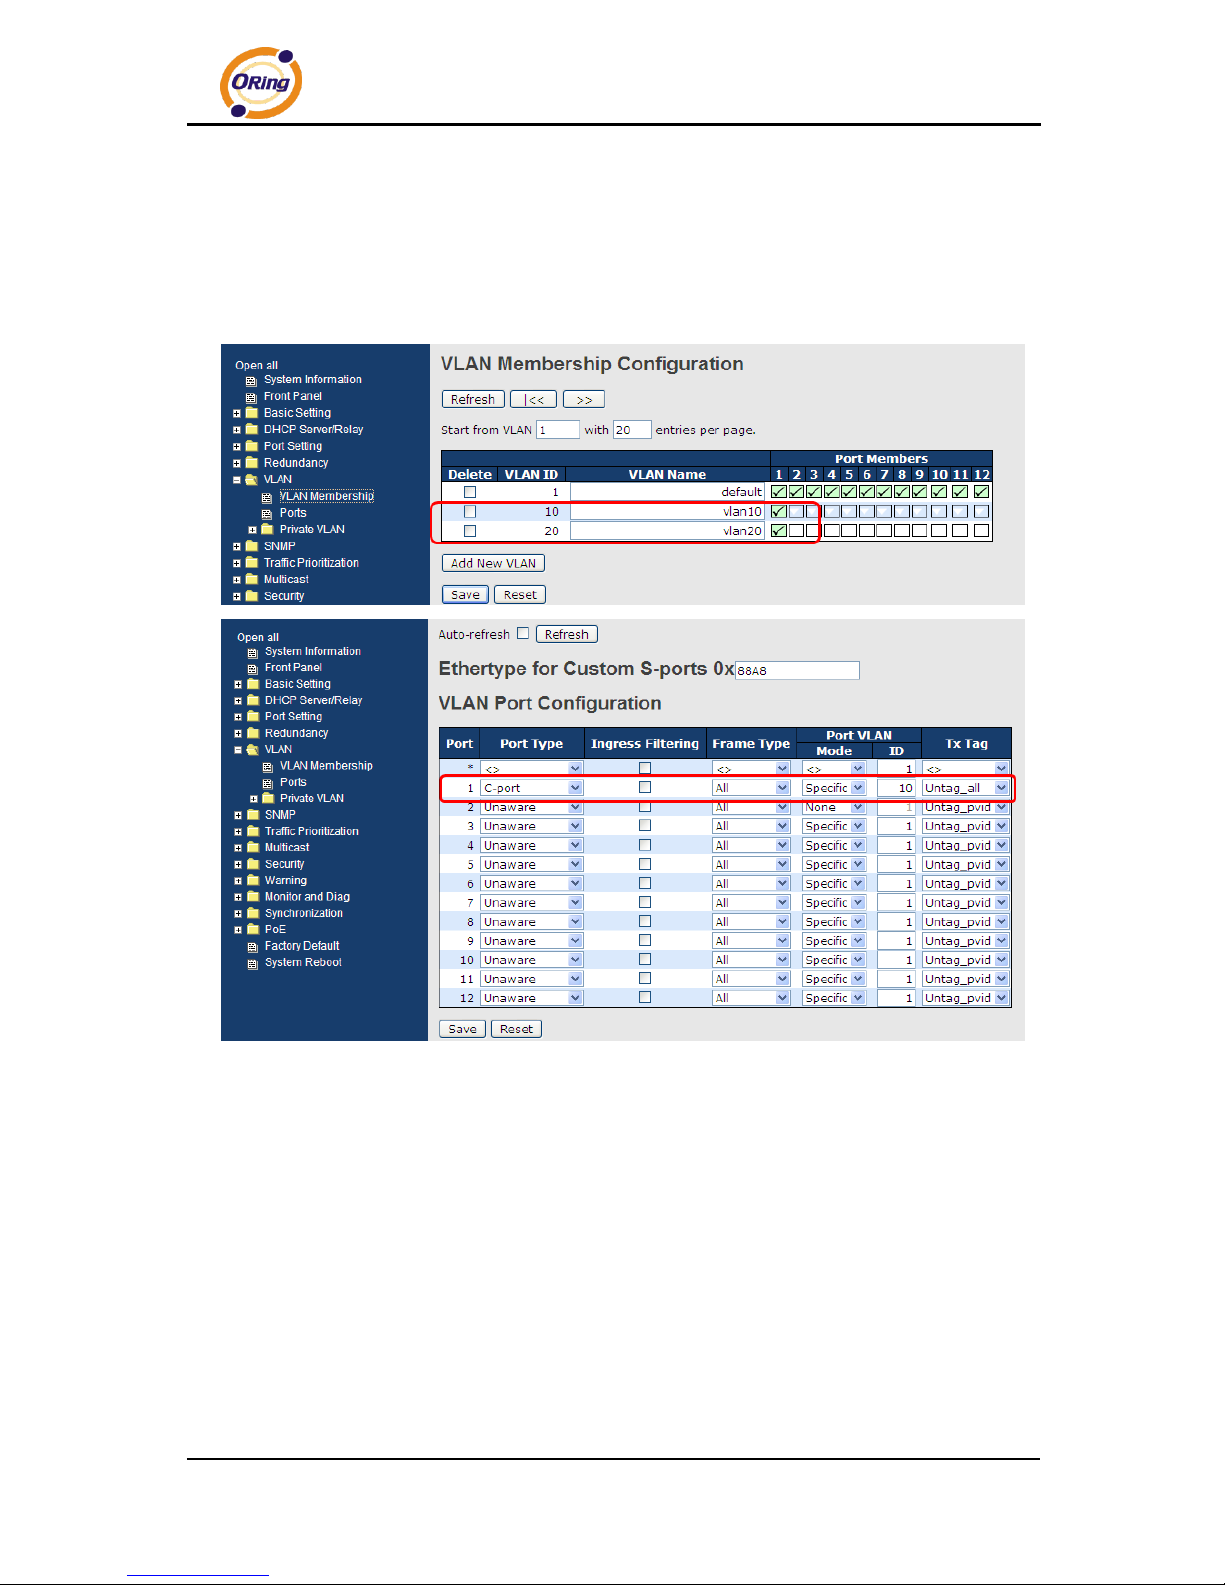
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
63
VLAN Hybrid Mode:
Port 1 VLAN Hybrid mode = untagged 10
Tagged 10, 20
Below are the switch settings.
Page 65
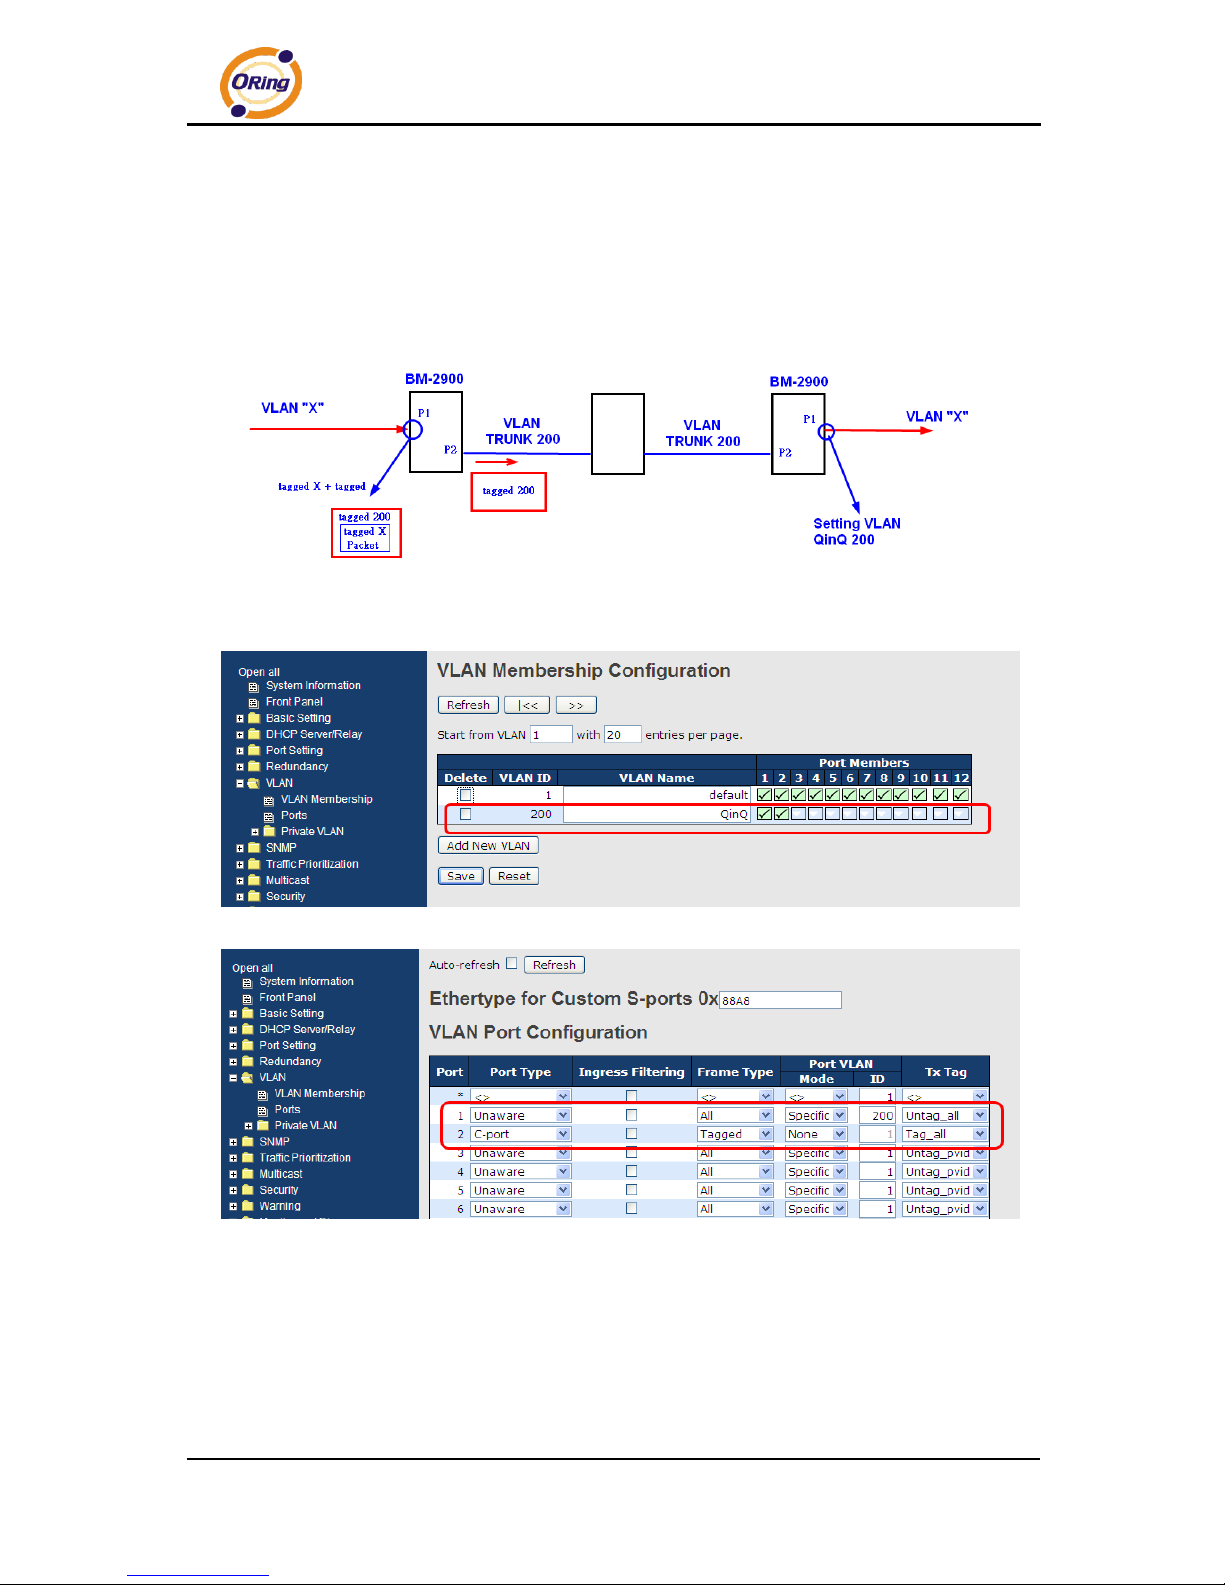
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
64
VLAN QinQ Mode:
VLAN QinQ mode is usually adopted when there are unknown VLANs, as shown in the figure
below.
VLAN “X” = Unknown VLAN
9000 Series Port 1 VLAN Settings:
Page 66
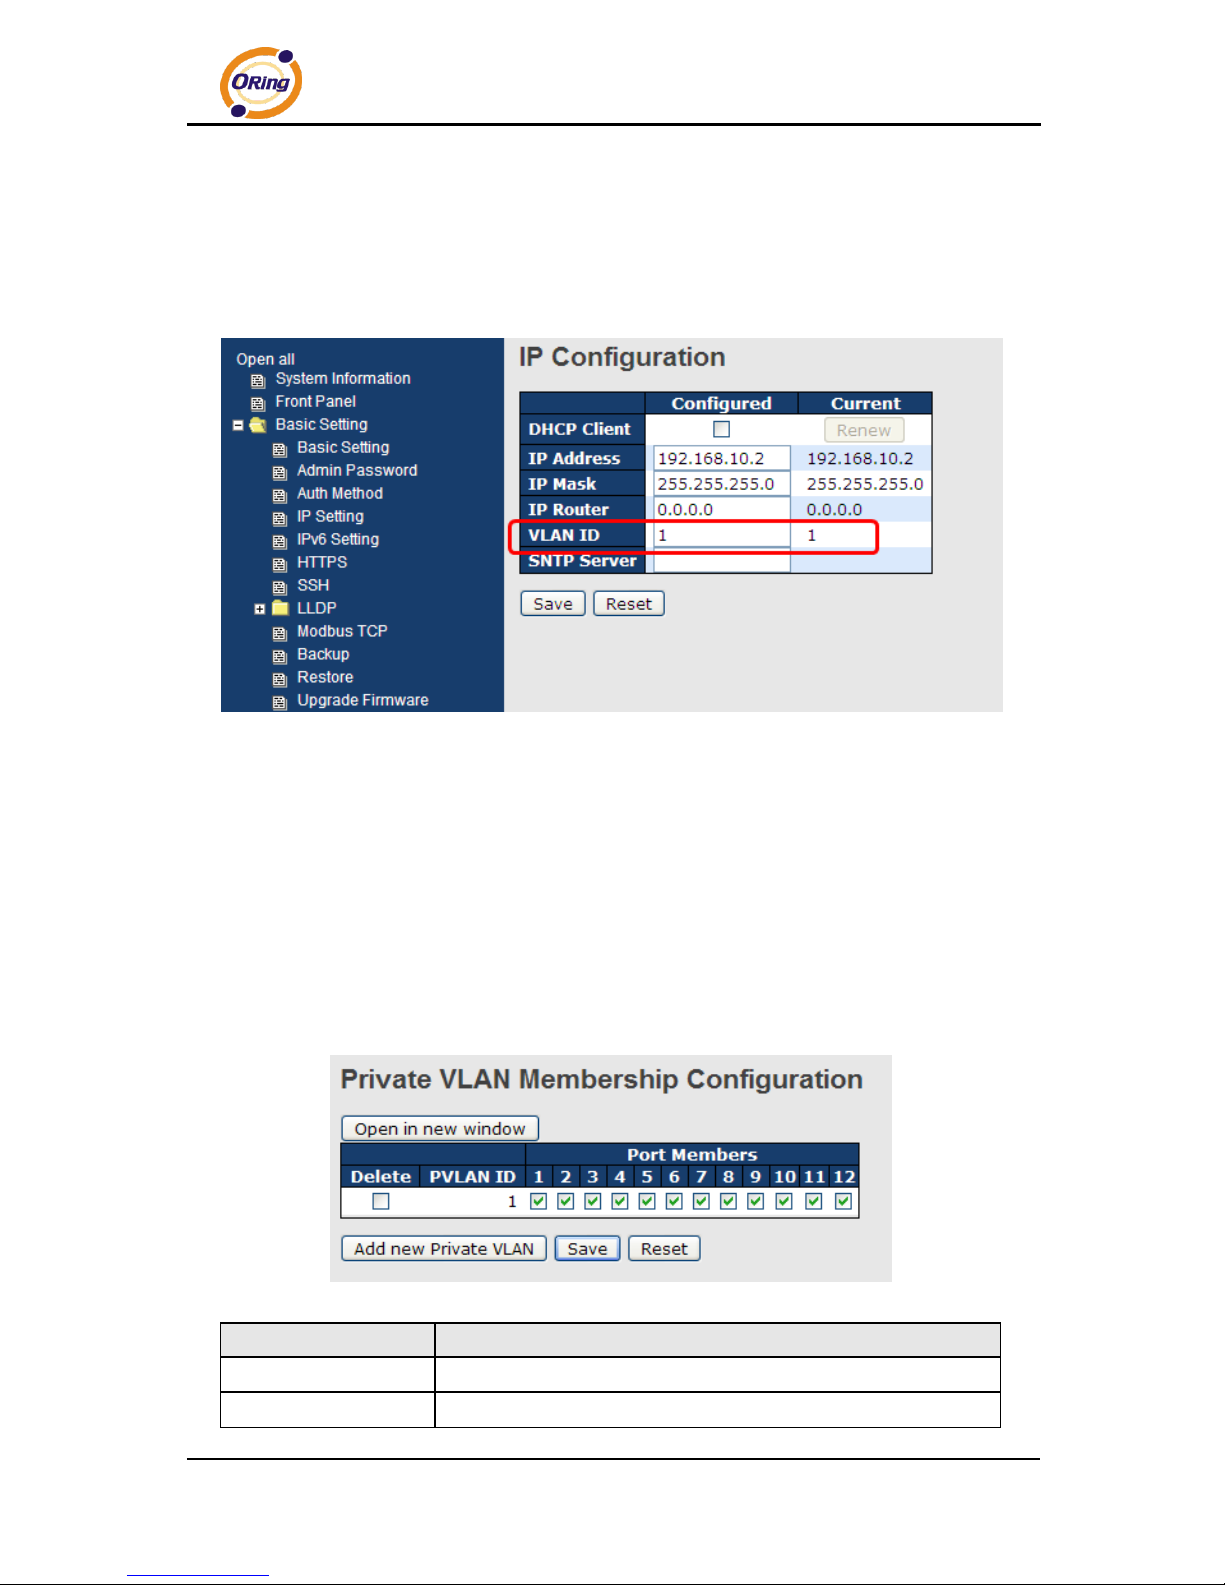
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
65
VLAN ID Settings
When setting the management VLAN, only the same VLAN ID port can be used to control the
switch.
9000 ies VLAN Settings:
5.4.3 Private VLAN
A private VLAN contains switch ports that can only communicate with a given "uplink". The
restricted ports are called private ports. Each private VLAN typically contains many private
ports and a single uplink. The switch forwards all frames received on a private port out the
uplink port, regardless of VLAN ID or destination MAC address. A port must be a member of
both a VLAN and a private VLAN to be able to forward packets. This page allows you to
configure private VLAN memberships for the switch. By default, all ports are VLAN unaware
and members of VLAN 1 and private VLAN 1.
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
Private VLAN ID
Indicates the ID of this particular private VLAN.
Page 67
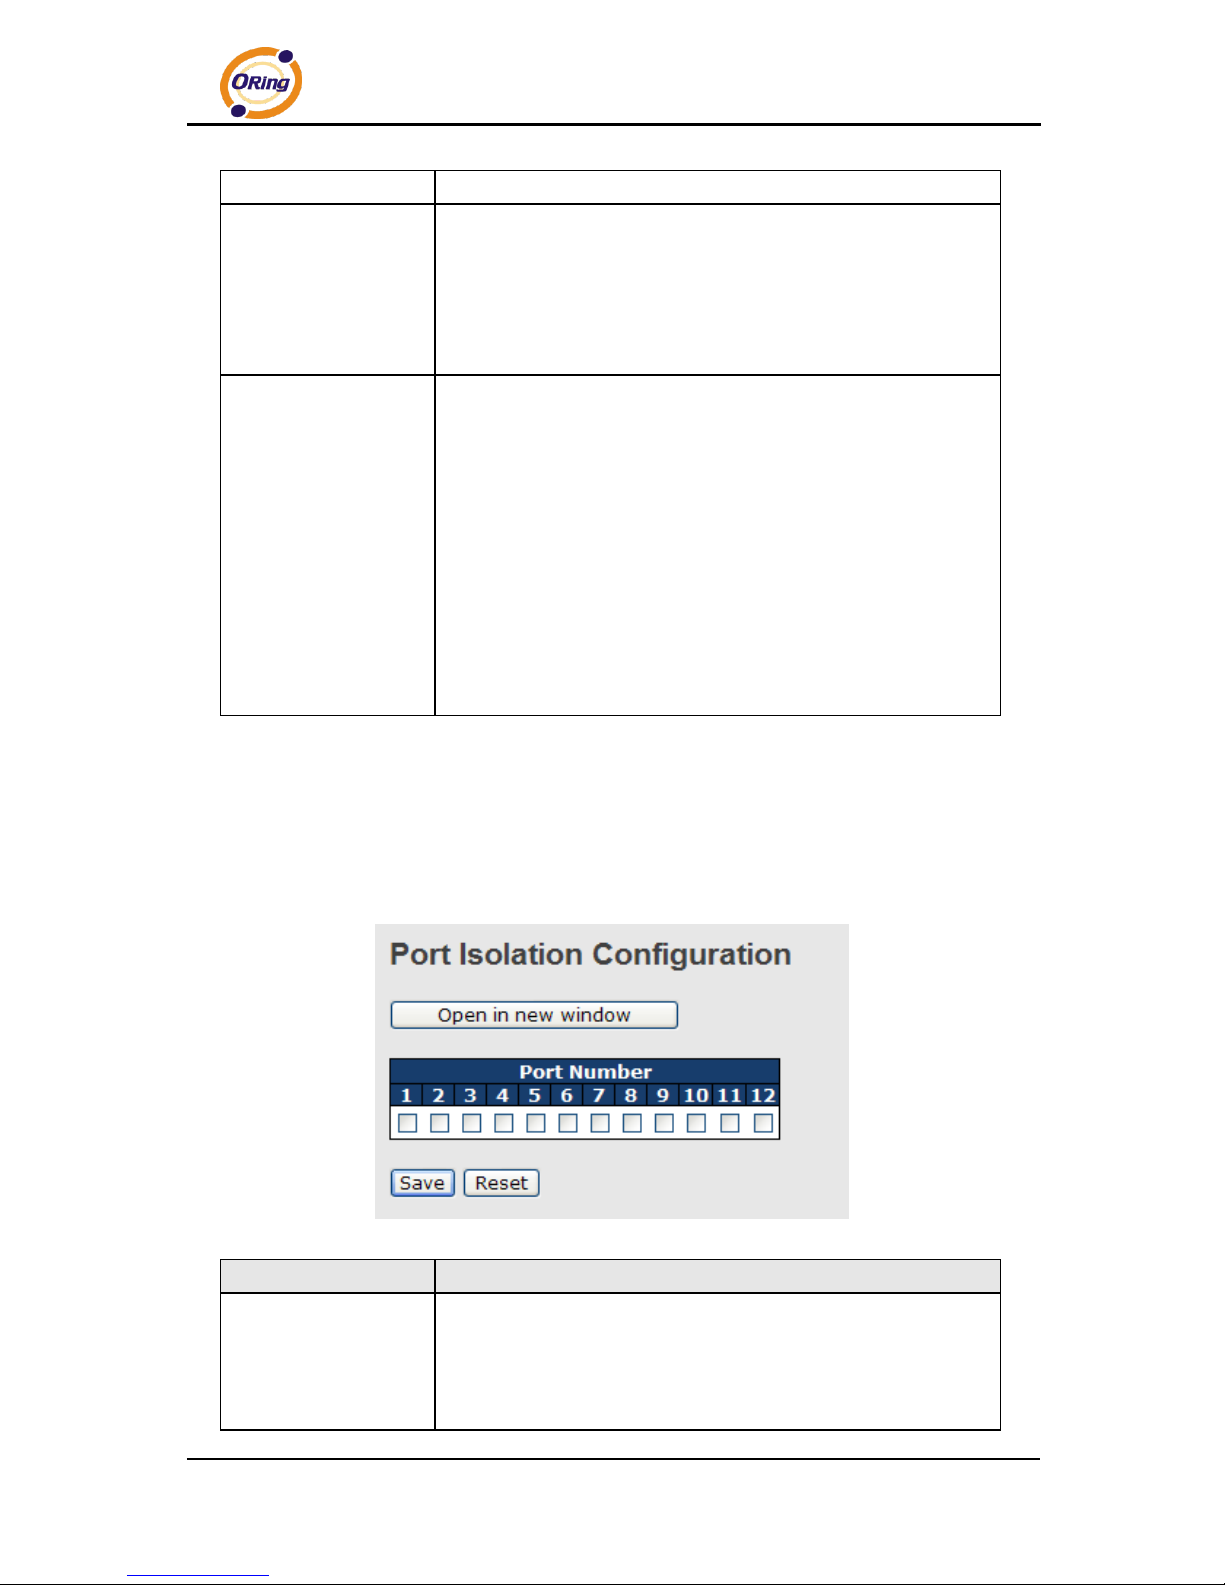
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
66
MAC Address
The MAC address for the entry.
Port Members
A row of check boxes for each port is displayed for each private
VLAN ID. You can check the box to include a port in a private
VLAN. To remove or exclude the port from the private VLAN,
make sure the box is unchecked. By default, no ports are
members, and all boxes are unchecked.
Adding a New Static
Entry
Click Add new Private VLAN to add a new private VLAN ID. An
empty row is added to the table, and the private VLAN can be
configured as needed. The allowed range for a private VLAN ID is
the same as the switch port number range. Any values outside
this range are not accepted, and a warning message appears.
Click OK to discard the incorrect entry, or click Cancel to return to
the editing and make a correction.
The private VLAN is enabled when you click Save.
The Delete button can be used to undo the addition of new
private VLANs.
A private VLAN is defined as a pairing of a primary VLAN with a secondary VLAN. A
promiscuous port is a port that can communicate with all other private VLAN port types via the
primary VLAN and any associated secondary VLANs, whereas isolated ports can
communicate only with a promiscuous port.
Label
Description
Port Members
A check box is provided for each port of a private VLAN.
When checked, port isolation is enabled for that port.
When unchecked, port isolation is disabled for that port.
By default, port isolation is disabled for all ports.
Page 68
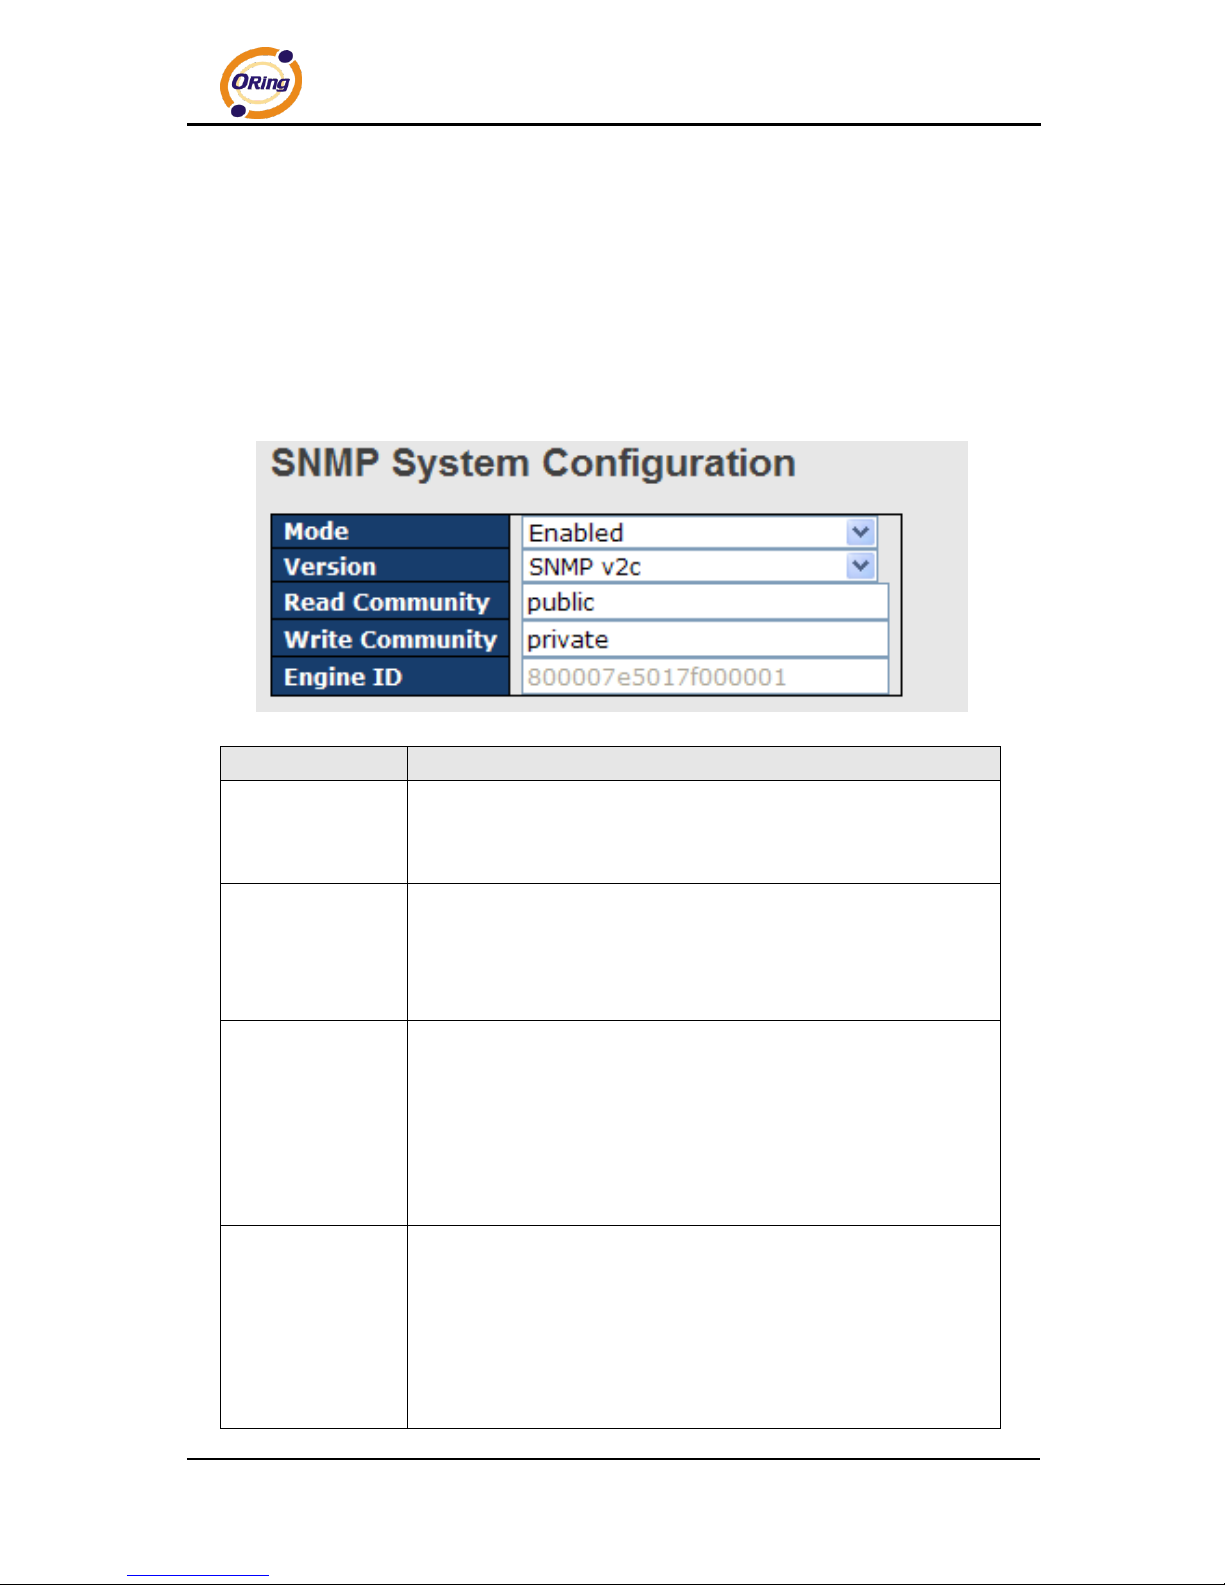
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
67
5.5 SNMP
SNMP (Simple Network Management Protocol) is a protocol for managing devices on IP
networks. It is mainly used network management systems to monitor the operational status of
networked devices. In an event-triggered situation, traps and notifications will be sent to
administrators.
5.5.1 SNMP System Configurations
Label
Description
Mode
Indicates existing SNMP mode. Possible modes include:
Enabled: enable SNMP mode
Disabled: disable SNMP mode
Version
Indicates the supported SNMP version. Possible versions include:
SNMP v1: supports SNMP version 1.
SNMP v2c: supports SNMP version 2c.
SNMP v3: supports SNMP version 3.
Read Community
Indicates the read community string to permit access to SNMP agent.
The allowed string length is 0 to 255, and only ASCII characters from
33 to 126 are allowed.
The field only suits to SNMPv1 and SNMPv2c. SNMPv3 uses USM
for authentication and privacy and the community string will be
associated with SNMPv3 community table.
Write Community
Indicates the write community string to permit access to SNMP
agent. The allowed string length is 0 to 255, and only ASCII
characters from 33 to 126 are allowed.
The field only suits to SNMPv1 and SNMPv2c. SNMPv3 uses USM
for authentication and privacy and the community string will be
associated with SNMPv3 community table.
Page 69
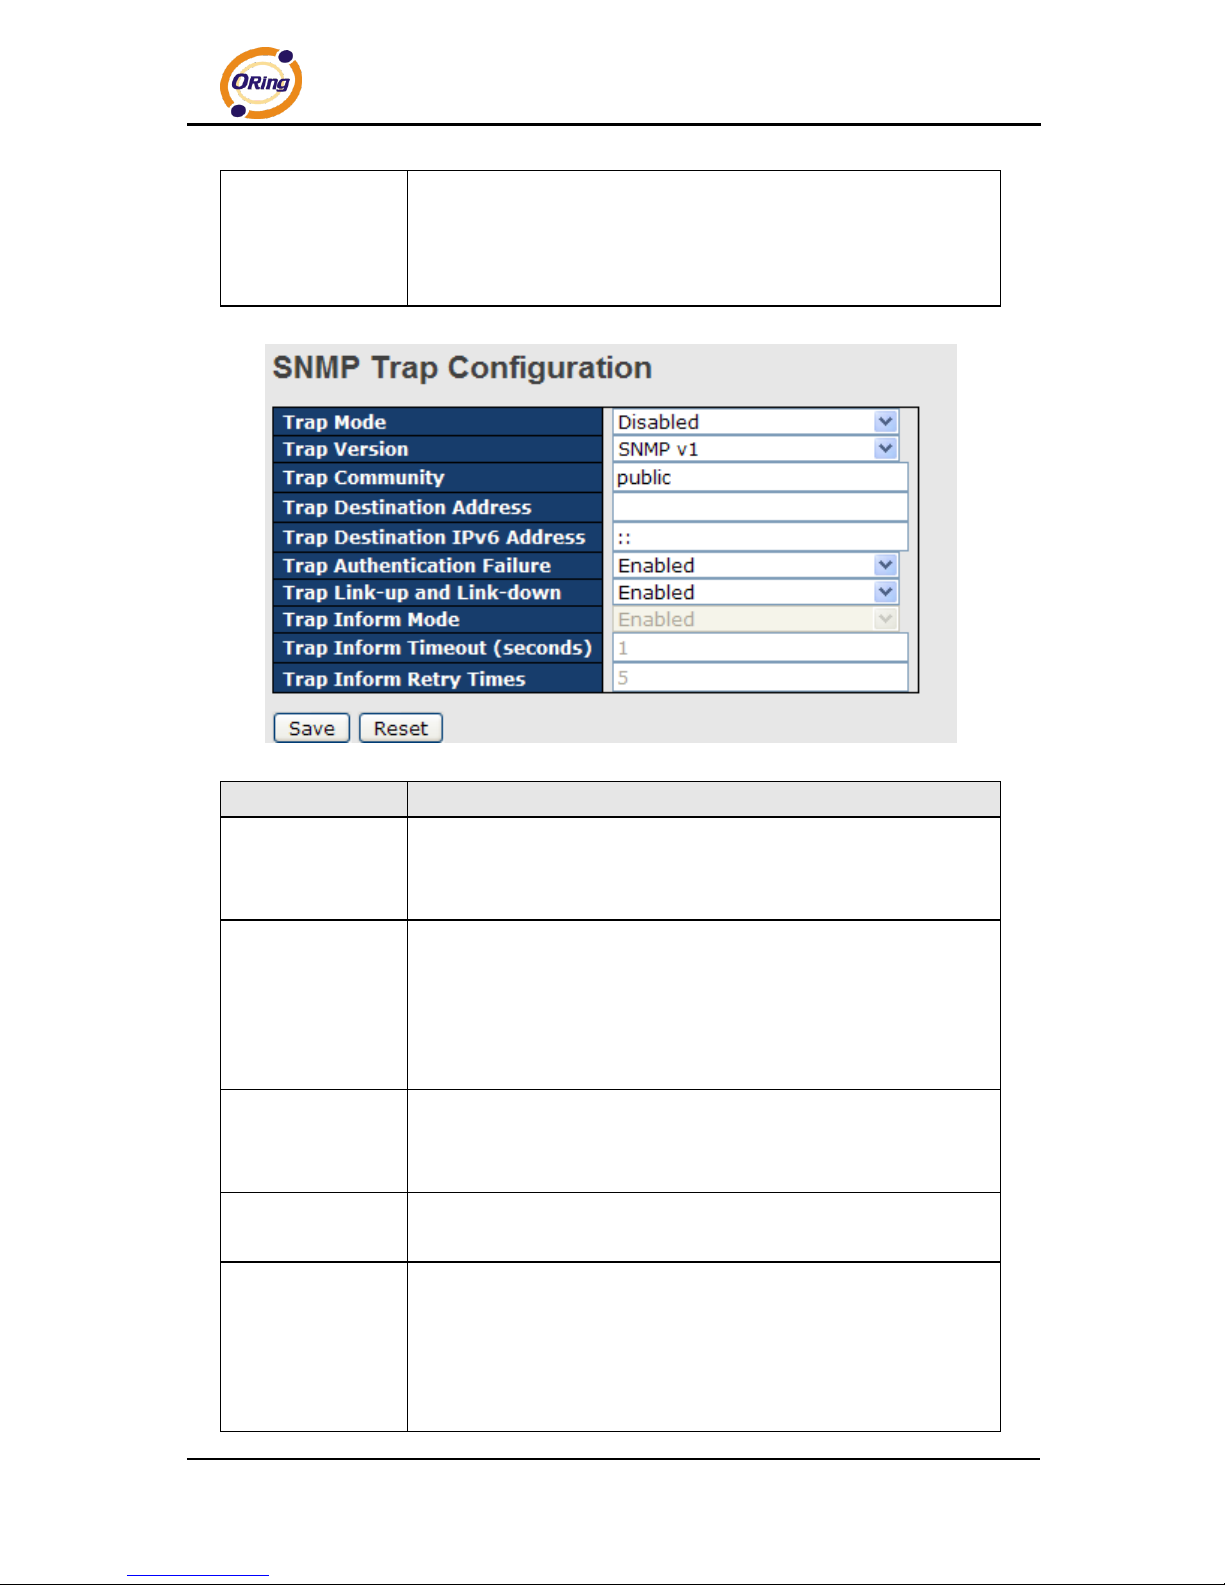
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
68
Engine ID
Indicates the SNMPv3 engine ID. The string must contain an even
number between 10 and 64 hexadecimal digits, but all-zeros and
all-'F's are not allowed. Change of the Engine ID will clear all original
local users.
Label
Description
Trap Mode
Indicates existing SNMP trap mode. Possible modes include:
Enabled: enable SNMP trap mode
Disabled: disable SNMP trap mode
Trap Version
Indicates the supported SNMP trap version. Possible versions
include:
SNMP v1: supports SNMP trap version 1
SNMP v2c: supports SNMP trap version 2c
SNMP v3: supports SNMP trap version 3
Trap Community
Indicates the community access string when sending SNMP trap
packets. The allowed string length is 0 to 255, and only ASCII
characters from 33 to 126 are allowed.
Trap Destination
Address
Indicates the SNMP trap destination address
Trap Destination
IPv6 Address
Provides the trap destination IPv6 address of this switch. IPv6
address consists of 128 bits represented as eight groups of four
hexadecimal digits with a colon separating each field (:). For
example, in 'fe80::215:c5ff:fe03:4dc7', the symbol '::' is a special
syntax that can be used as a shorthand way of representing multiple
Page 70
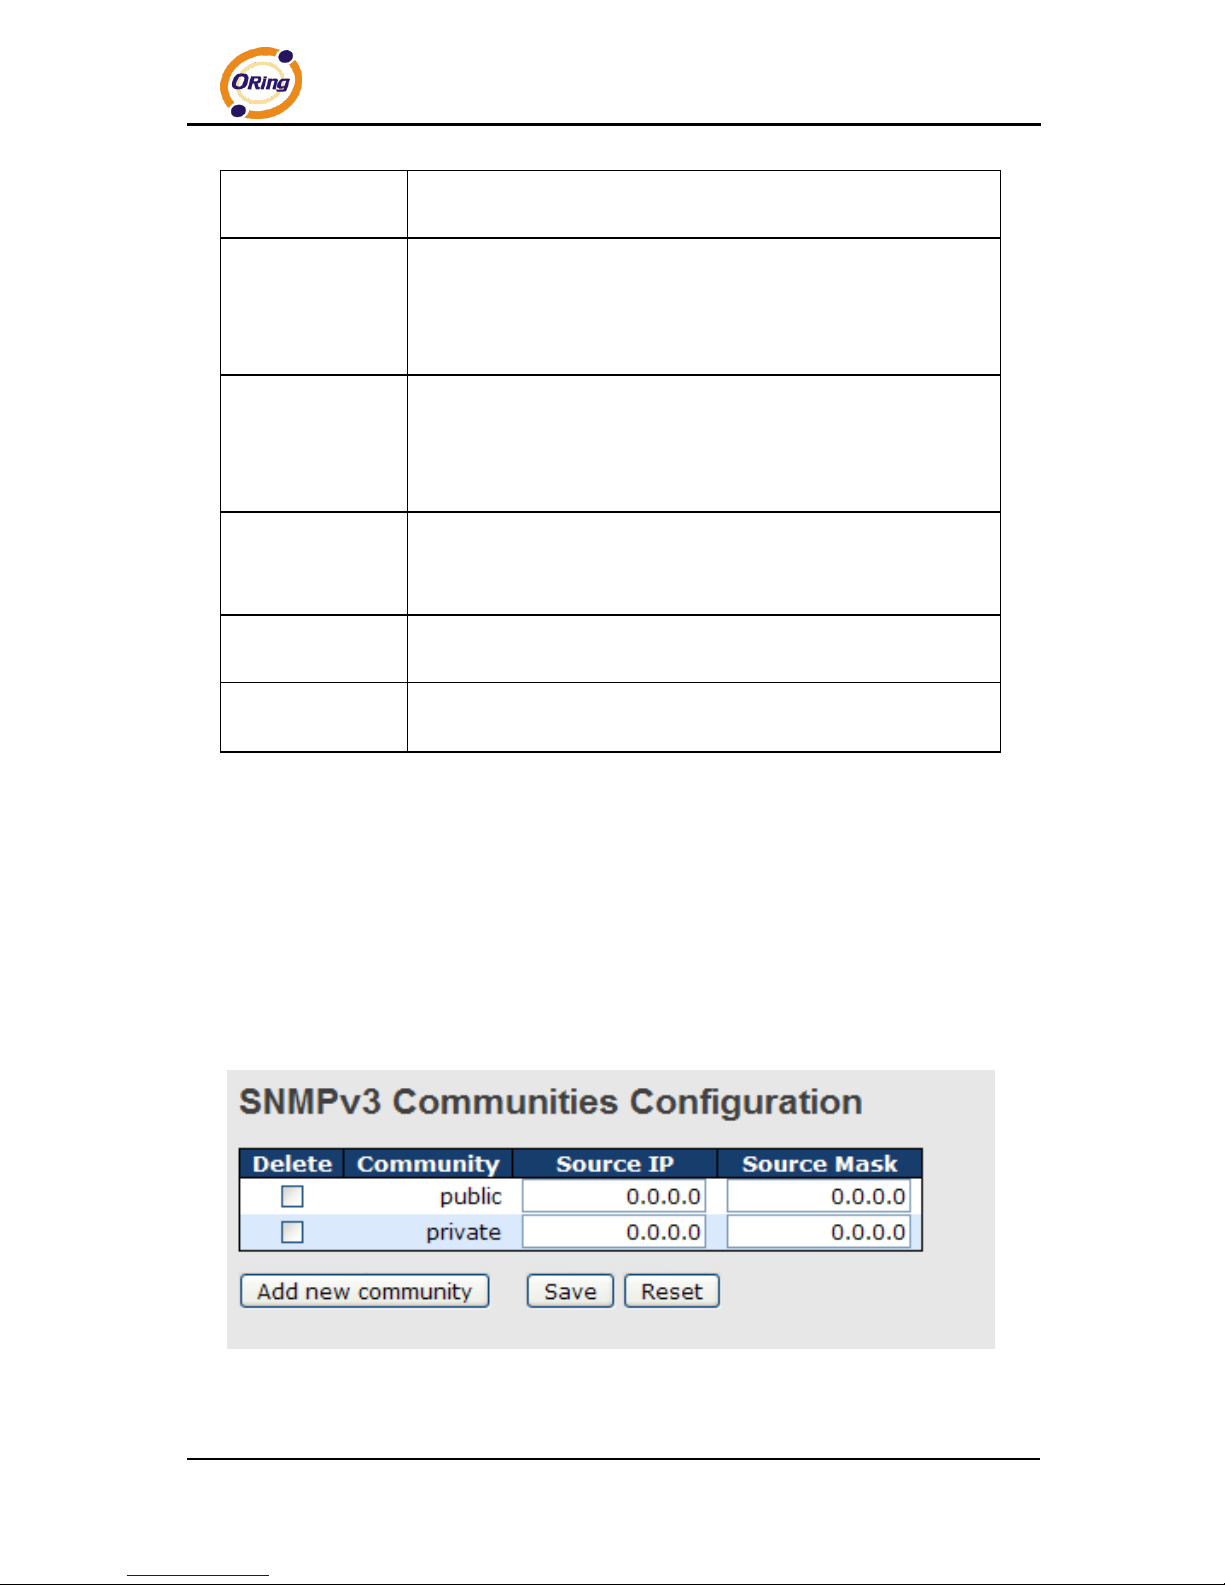
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
69
16-bit groups of contiguous zeros; but it can only appear once. It also
uses a following legally IPv4 address. For example, '::192.1.2.34'.
Trap
Authentication
Failure
Indicates the SNMP entity is permitted to generate authentication
failure traps. Possible modes include:
Enabled: enable SNMP trap authentication failure
Disabled: disable SNMP trap authentication failure
Trap Link-up and
Link-down
Indicates the SNMP trap link-up and link-down mode. Possible
modes include:
Enabled: enable SNMP trap link-up and link-down mode
Disabled: disable SNMP trap link-up and link-down mode
Trap Inform Mode
Indicates the SNMP trap inform mode. Possible modes include:
Enabled: enable SNMP trap inform mode
Disabled: disable SNMP trap inform mode
Trap Inform
Timeout(seconds)
Configures the SNMP trap inform timeout. The allowed range is 0 to
2147.
Trap Inform Retry
Times
Configures the retry times for SNMP trap inform. The allowed range
is 0 to 255.
5.5.2 SNMP Community Configurations
You can define access to the SNMP data on your devices by creating one or more SNMP
communities. An SNMP community is the group that devices and management stations
running SNMP belong to. It helps define where information is sent. A SNMP device or agent
may belong to more than one SNMP community. It will not respond to requests from
management stations that do not belong to one of its communities. This page allows you to
configure SNMPv3 community table. The entry index key is Community.
Page 71
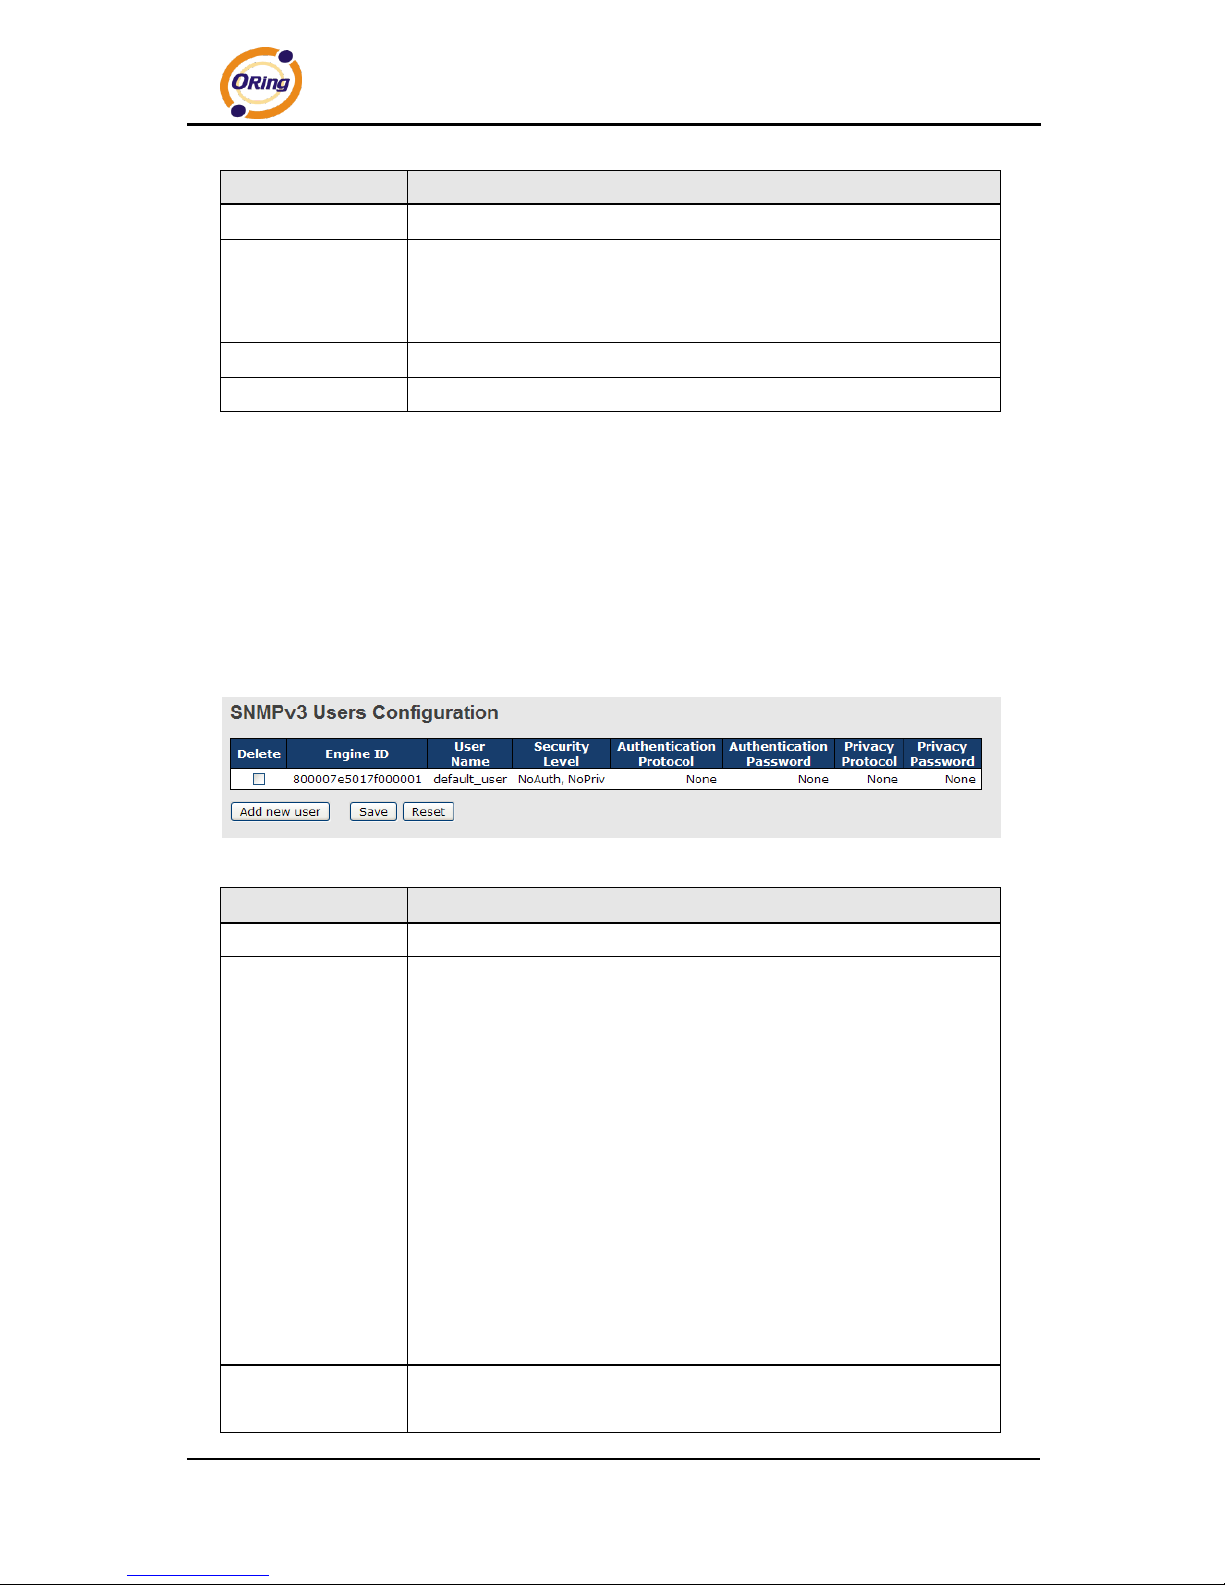
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
70
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
Community
Indicates the community access string to permit access to SNMPv3
agent. The allowed string length is 1 to 32, and only ASCII characters
from 33 to 126 are allowed.
Source IP
Indicates the SNMP source address
Source Mask
Indicates the SNMP source address mask
5.5.3 SNMP User Configurations
Each SNMP user has a specified username, a group to which the user belongs,
authentication password, authentication protocol, privacy protocol, and privacy password.
When you create a user, you must associate it with an SNMP group. The user then
inherits the security model of the group. This page allows you to configure the SNMPv3 user
table. The entry index keys are Engine ID and User Name.
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
Engine ID
An octet string identifying the engine ID that this entry should belong
to. The string must contain an even number between 10 and 64
hexadecimal digits, but all-zeros and all-'F's are not allowed. The
SNMPv3 architecture uses User-based Security Model (USM) for
message security and View-based Access Control Model (VACM) for
access control. For the USM entry, the usmUserEngineID and
usmUserName are the entry keys. In a simple agent,
usmUserEngineID is always that agent's own snmpEngineID value.
The value can also take the value of the snmpEngineID of a remote
SNMP engine with which this user can communicate. In other words,
if user engine ID is the same as system engine ID, then it is local
user; otherwise it's remote user.
User Name
A string identifying the user name that this entry should belong to.
The allowed string length is 1 to 32, and only ASCII characters from
Page 72
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
71
33 to 126 are allowed.
Security Level
Indicates the security model that this entry should belong to. Possible
security models include:
NoAuth, NoPriv: no authentication and none privacy
Auth, NoPriv: Authentication and no privacy
Auth, Priv: Authentication and privacy
The value of security level cannot be modified if the entry already
exists, which means the value must be set correctly at the time of
entry creation.
Authentication
Protocol
Indicates the authentication protocol that this entry should belong to.
Possible authentication protocols include:
None: no authentication protocol
MD5: an optional flag to indicate that this user is using MD5
authentication protocol
SHA: an optional flag to indicate that this user is using SHA
authentication protocol
The value of security level cannot be modified if the entry already
exists, which means the value must be set correctly at the time of
entry creation.
Authentication
Password
A string identifying the authentication pass phrase. For MD5
authentication protocol, the allowed string length is 8 to 32. For SHA
authentication protocol, the allowed string length is 8 to 40. Only
ASCII characters from 33 to 126 are allowed.
Privacy Protocol
Indicates the privacy protocol that this entry should belong to.
Possible privacy protocols include:
None: no privacy protocol
DES: an optional flag to indicate that this user is using DES
authentication protocol
Privacy Password
A string identifying the privacy pass phrase. The allowed string length
is 8 to 32, and only ASCII characters from 33 to 126 are allowed.
5.5.4 SNMP Group Configurations
An SNMP group is an access control policy for you to add users. Each SNMP group is
configured with a security model, and is associated with an SNMP view. A user within an
SNMP group should match the security model of the SNMP group. These parameters specify
what type of authentication and privacy a user within an SNMP group uses. Each SNMP group
name and security model pair must be unique. This page allows you to configure the SNMPv3
Page 73
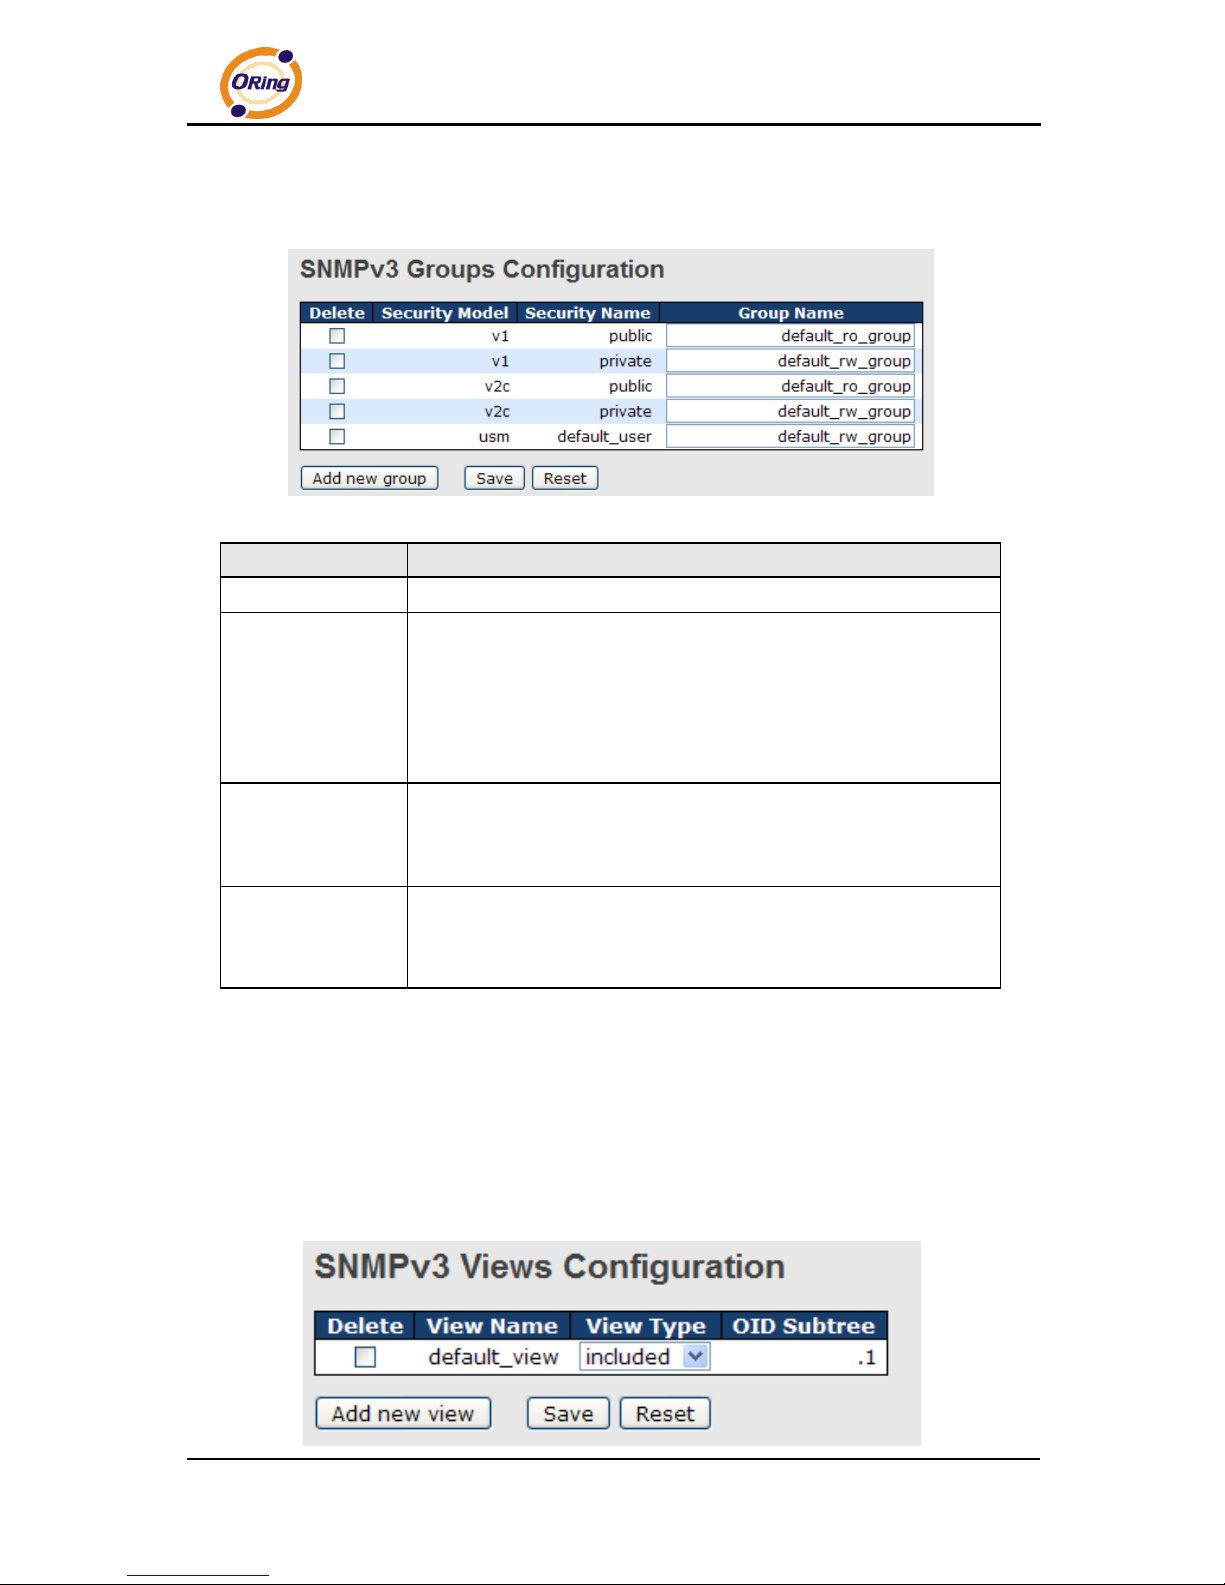
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
72
group table. The entry index keys are Security Model and Security Name.
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
Security Model
Indicates the security model that this entry should belong to. Possible
security models included:
v1: Reserved for SNMPv1.
v2c: Reserved for SNMPv2c.
usm: User-based Security Model (USM).
Security Name
A string identifying the security name that this entry should belong to.
The allowed string length is 1 to 32, and only ASCII characters from
33 to 126 are allowed.
Group Name
A string identifying the group name that this entry should belong to.
The allowed string length is 1 to 32, and only ASCII characters from
33 to 126 are allowed.
5.5.5 SNMP View Configurations
The SNMP v3 View table specifies the MIB object access requirements for each View Name.
You can specify specific areas of the MIB that can be accessed or denied based on the entries
or create and delete entries in the View table in this page. The entry index keys are View
Name and OID Subtree.
Page 74
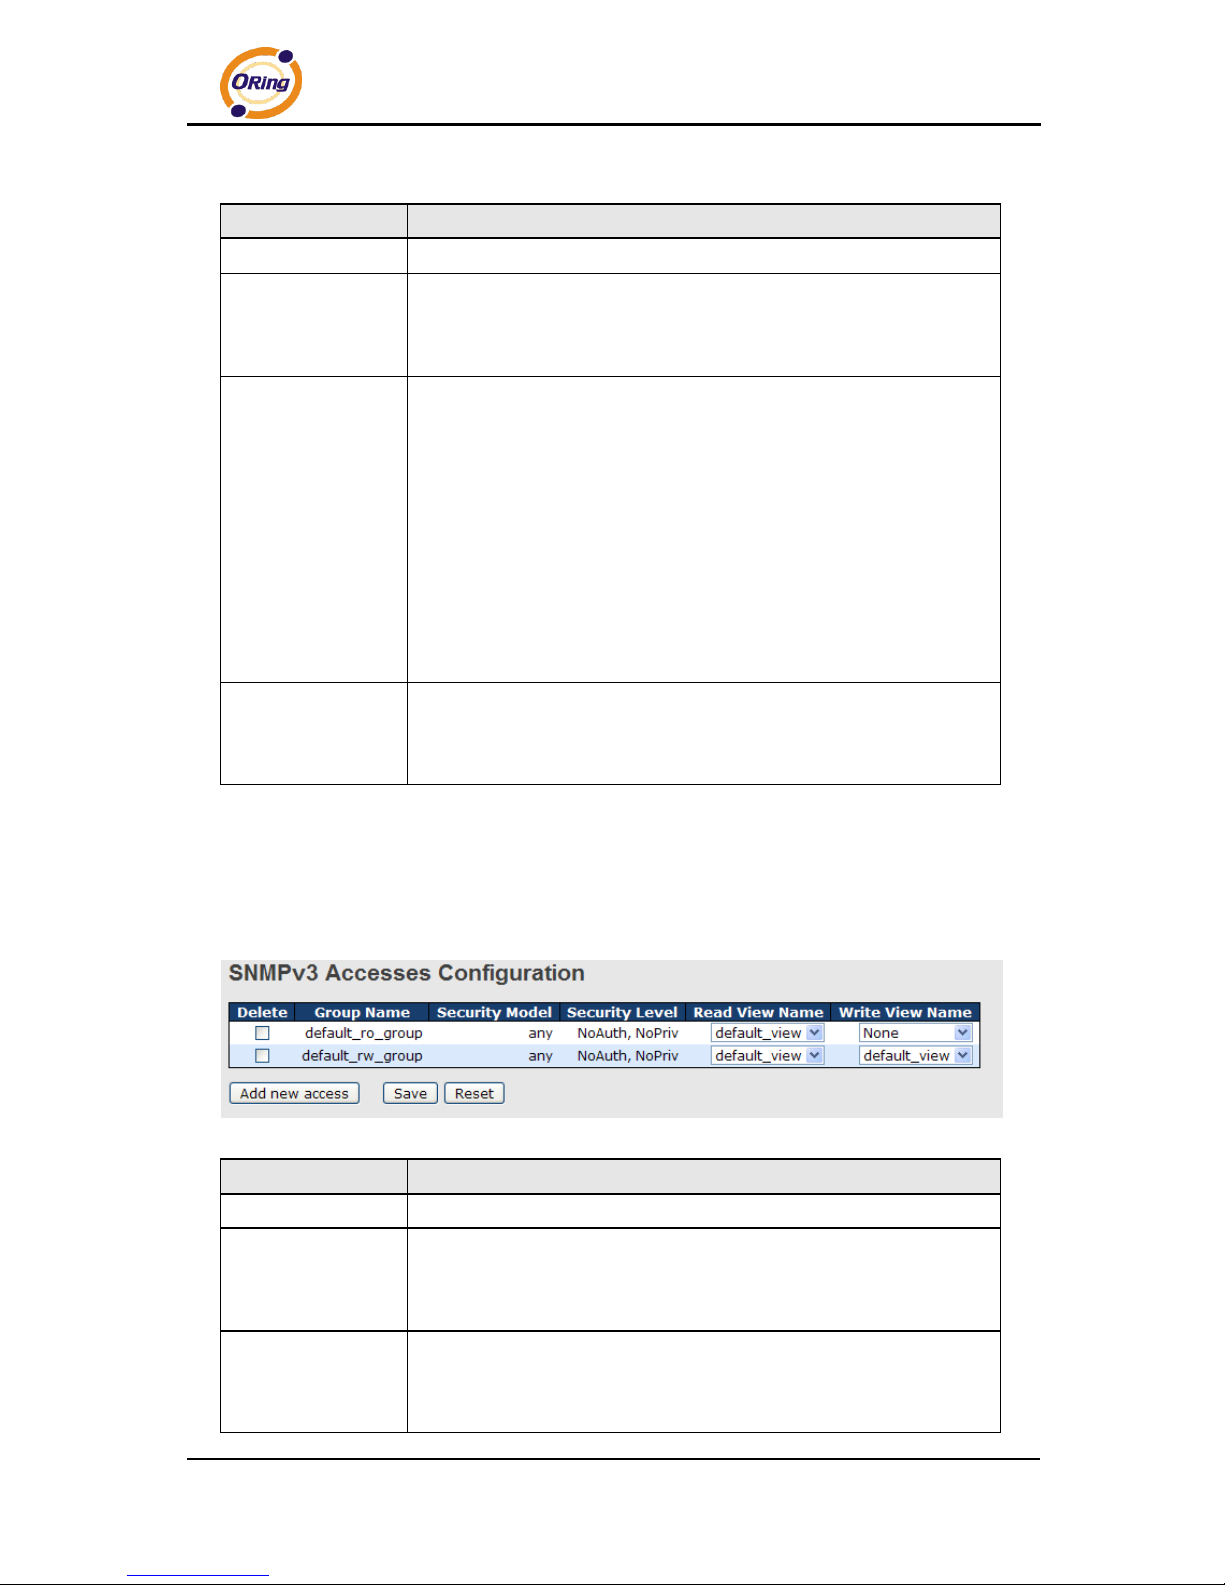
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
73
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
View Name
A string identifying the view name that this entry should belong to.
The allowed string length is 1 to 32, and only ASCII characters from
33 to 126 are allowed.
View Type
Indicates the view type that this entry should belong to. Possible view
types include:
Included: an optional flag to indicate that this view subtree should be
included.
Excluded: An optional flag to indicate that this view subtree should
be excluded.
Generally, if an entry's view type is Excluded, it should exist another
entry whose view type is Included, and its OID subtree oversteps
the Excluded entry.
OID Subtree
The OID defining the root of the subtree to add to the named view.
The allowed OID length is 1 to 128. The allowed string content is
digital number or asterisk (*).
5.5.6 SNMP Access Configurations
This page allows you to configure SNMPv3 access table. The entry index keys are Group
Name, Security Model, and Security Level.
Label
Description
Delete
Check to delete the entry. It will be deleted during the next save.
Group Name
A string identifying the group name that this entry should belong to.
The allowed string length is 1 to 32, and only ASCII characters from
33 to 126 are allowed.
Security Model
Indicates the security model that this entry should belong to. Possible
security models include:
any: Accepted any security model (v1|v2c|usm).
Page 75
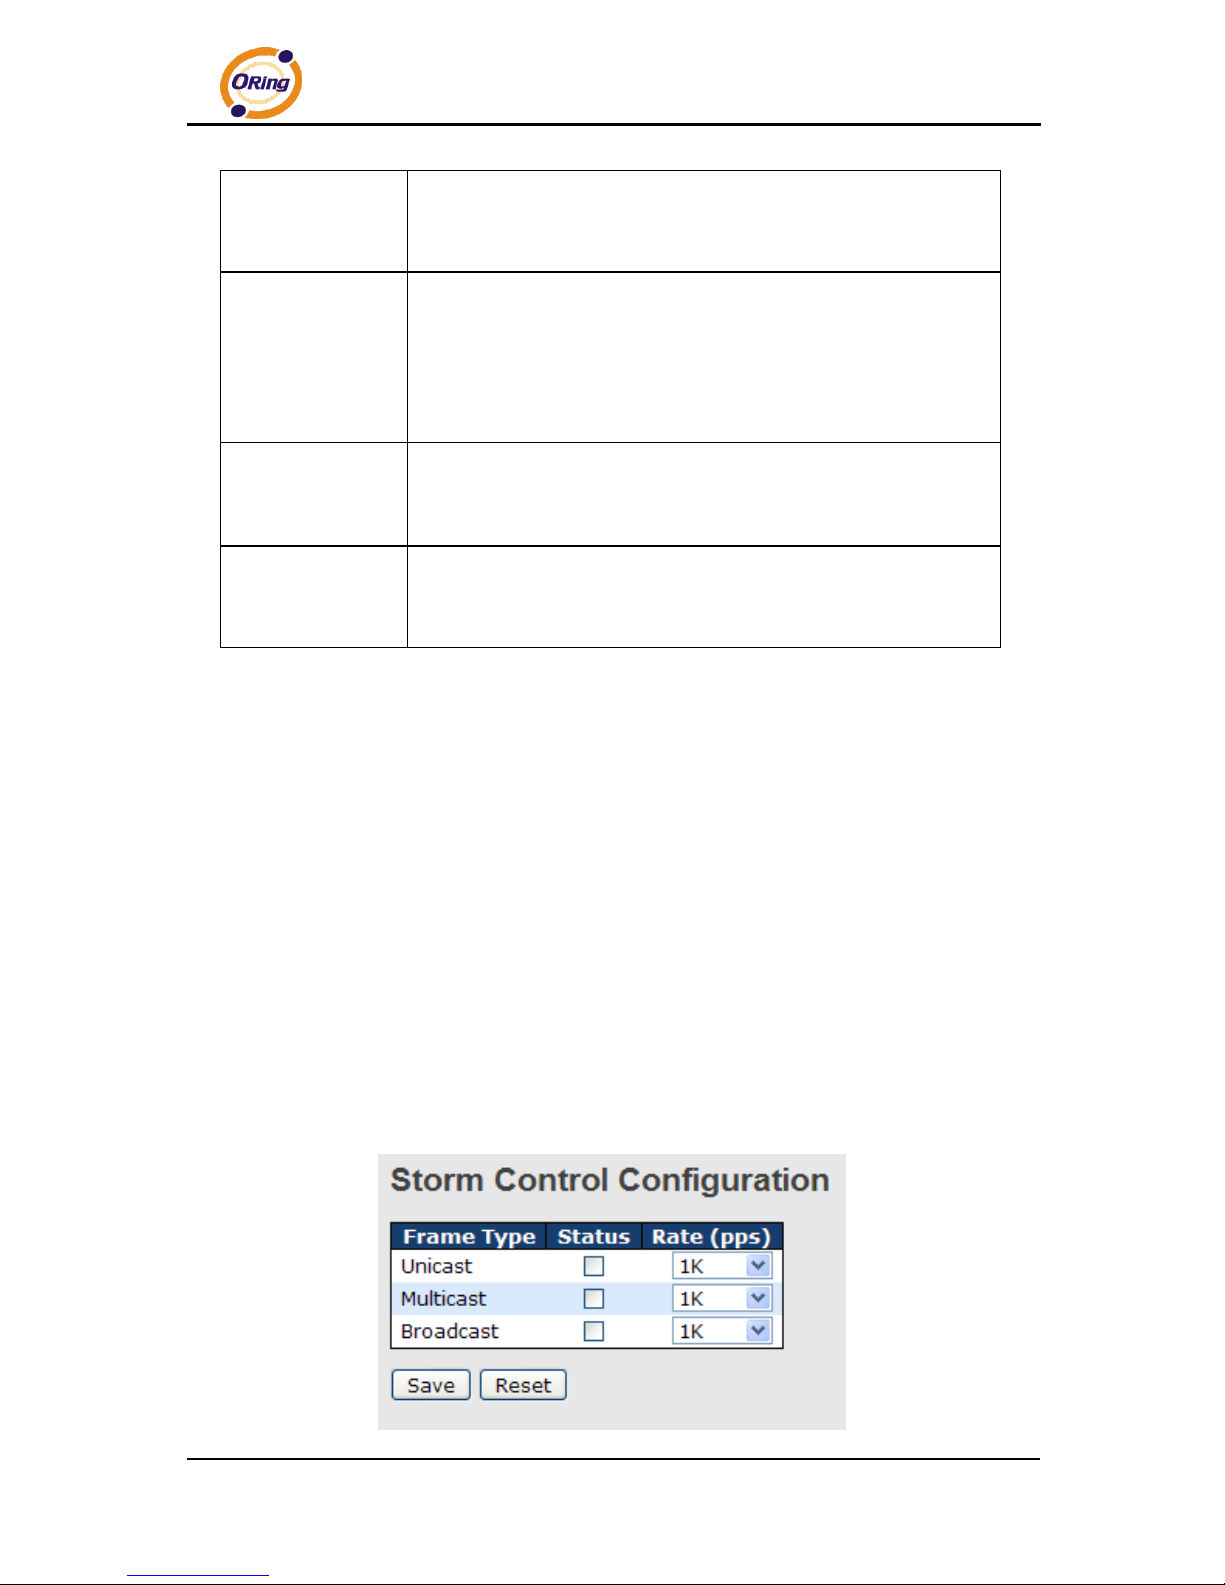
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
74
v1: Reserved for SNMPv1.
v2c: Reserved for SNMPv2c.
usm: User-based Security Model (USM).
Security Level
Indicates the security model that this entry should belong to. Possible
security models include:
NoAuth, NoPriv: no authentication and no privacy
Auth, NoPriv: Authentication and no privacy
Auth, Priv: Authentication and privacy
Read View Name
The name of the MIB view defining the MIB objects for which this
request may request the current values. The allowed string length is
1 to 32, and only ASCII characters from 33 to 126 are allowed.
Write View Name
The name of the MIB view defining the MIB objects for which this
request may potentially SET new values. The allowed string length is
1 to 32, and only ASCII characters from 33 to 126 are allowed.
5.6 Traffic Prioritization
5.6.1 Storm Control
A LAN storm occurs when packets flood the LAN, creating excessive traffic and degrading
network performance. Errors in the protocol-stack implementation, mistakes in network
configuration, or users issuing a denial-of-service attack can cause a storm. Storm control
prevents traffic on a LAN from being disrupted by a broadcast, multicast, or unicast storm on a
port. In this page, you can specify the rate at which packets are received for unicast,
multicast, and broadcast traffic. The unit of the rate can be either pps (packets per second) or
kpps (kilopackets per second).
Note: frames sent to the CPU of the switch are always limited to approximately 4 kpps. For
example, broadcasts in the management VLAN are limited to this rate. The management
VLAN is configured on the IP setup page.
Page 76
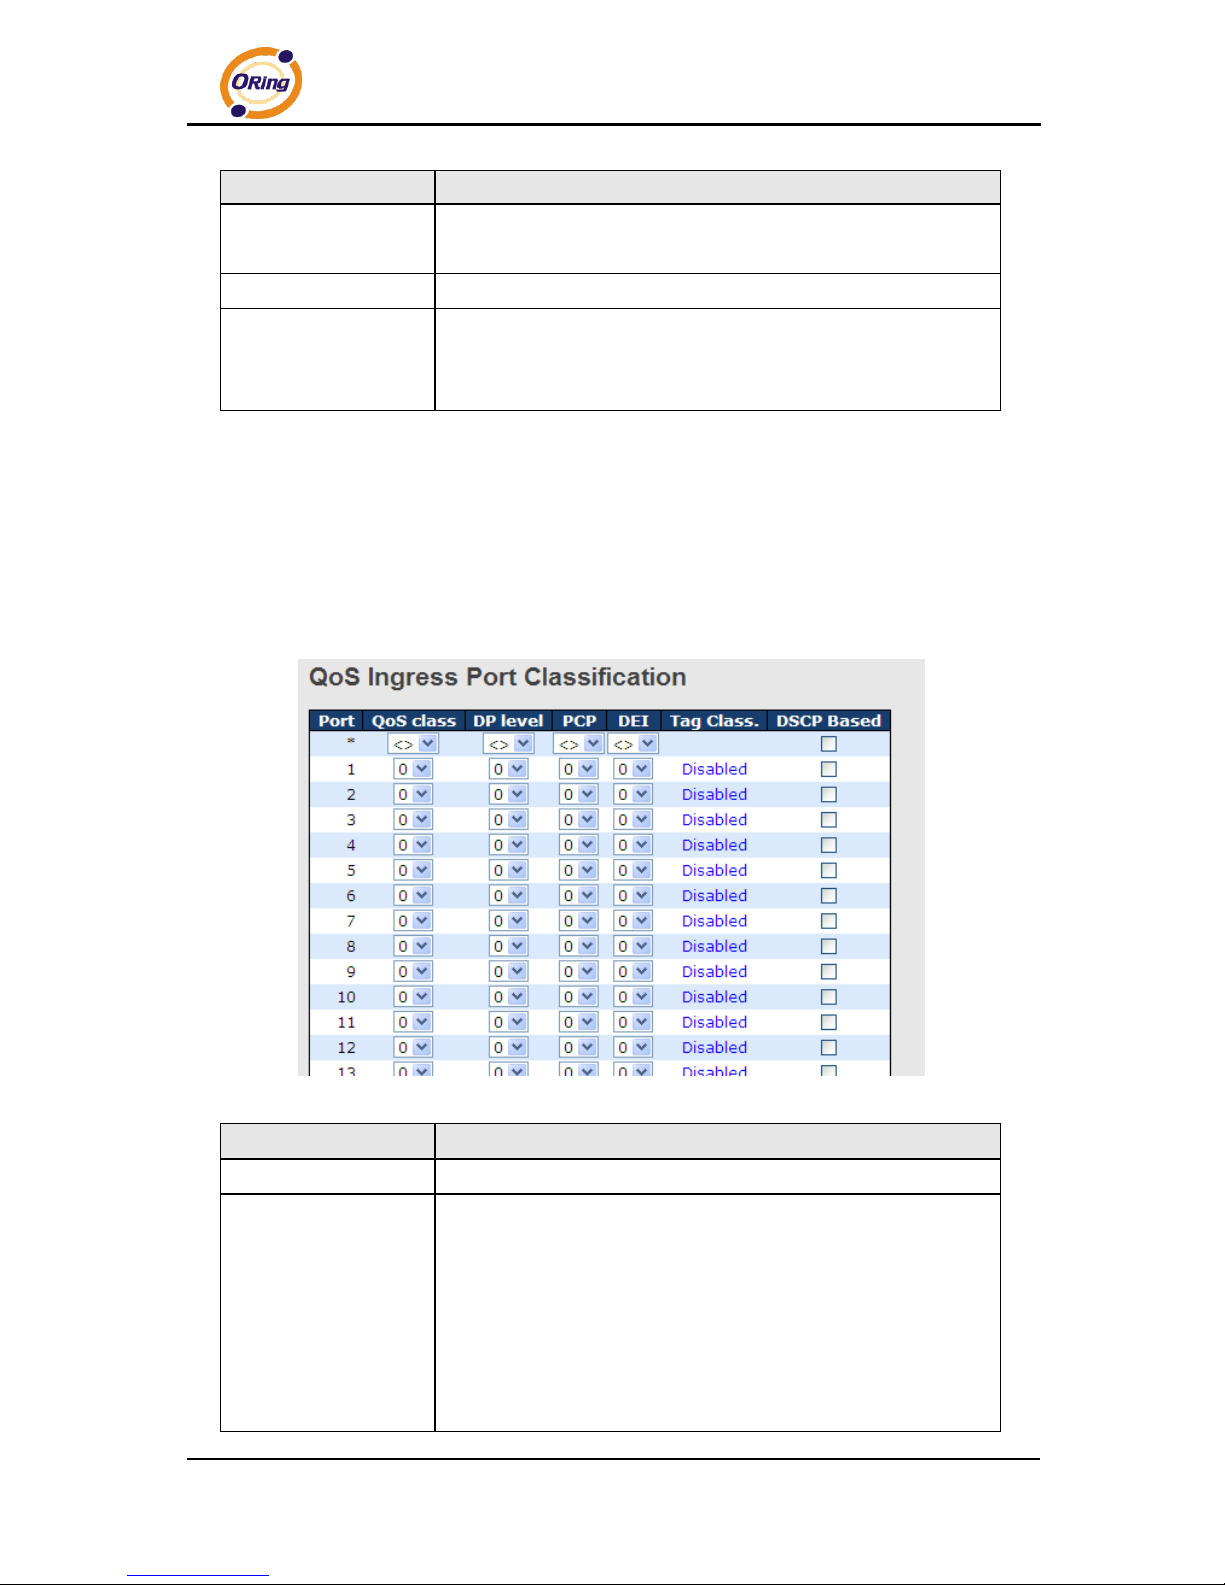
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
75
Label
Description
Frame Type
Frame types supported by the Storm Control function, including
Unicast, Multicast, and Broadcast.
Status
Enables or disables the given frame type
Rate
The rate is packet per second (pps), configure the rate as 1K, 2K,
4K, 8K, 16K, 32K, 64K, 128K, 256K, 512K, or 1024K.
The 1 kpps is actually 1002.1 pps.
5.6.2 Port Classification
QoS (Quality of Service) is a method to achieve efficient bandwidth utilization between devices
by prioritizing frames according to individual requirements and transmit the frames based on
their importance. Frames in higher priority queues receive a bigger slice of bandwidth than
those in a lower priority queue.
Label
Description
Port
The port number for which the configuration below applies
QoS Class
Controls the default QoS class
All frames are classified to a QoS class. There is a one to one
mapping between QoS class, queue, and priority. A QoS class of
0 (zero) has the lowest priority.
If the port is VLAN aware and the frame is tagged, then the frame
is classified to a QoS class that is based on the PCP value in the
tag as shown below. Otherwise the frame is classified to the
Page 77
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
76
default QoS class.
PCP value: 0 1 2 3 4 5 6 7
QoS class: 1 0 2 3 4 5 6 7
If the port is VLAN aware, the frame is tagged, and Tag Class is
enabled, then the frame is classified to a QoS class that is
mapped from the PCP and DEI value in the tag. Otherwise the
frame is classified to the default QoS class.
The classified QoS class can be overruled by a QCL entry.
Note: if the default QoS class has been dynamically changed,
then the actual default QoS class is shown in parentheses after
the configured default QoS class.
DP level
Controls the default Drop Precedence Level
All frames are classified to a DP level.
If the port is VLAN aware and the frame is tagged, then the frame
is classified to a DP level that is equal to the DEI value in the tag.
Otherwise the frame is classified to the default DP level.
If the port is VLAN aware, the frame is tagged, and Tag Class is
enabled, then the frame is classified to a DP level that is mapped
from the PCP and DEI value in the tag. Otherwise the frame is
classified to the default DP level.
The classified DP level can be overruled by a QCL entry.
PCP
Controls the default PCP value
All frames are classified to a PCP value.
If the port is VLAN aware and the frame is tagged, then the frame
is classified to the PCP value in the tag. Otherwise the frame is
classified to the default PCP value.
DEI
Controls the default DEI value
All frames are classified to a DEI value.
If the port is VLAN aware and the frame is tagged, then the frame
is classified to the DEI value in the tag. Otherwise the frame is
classified to the default DEI value.
Tag Class
Shows the classification mode for tagged frames on this port
Disabled: Use default QoS class and DP level for tagged frames
Enabled: Use mapped versions of PCP and DEI for tagged
frames
Click on the mode to configure the mode and/or mapping
Note: this setting has no effect if the port is VLAN unaware.
Page 78
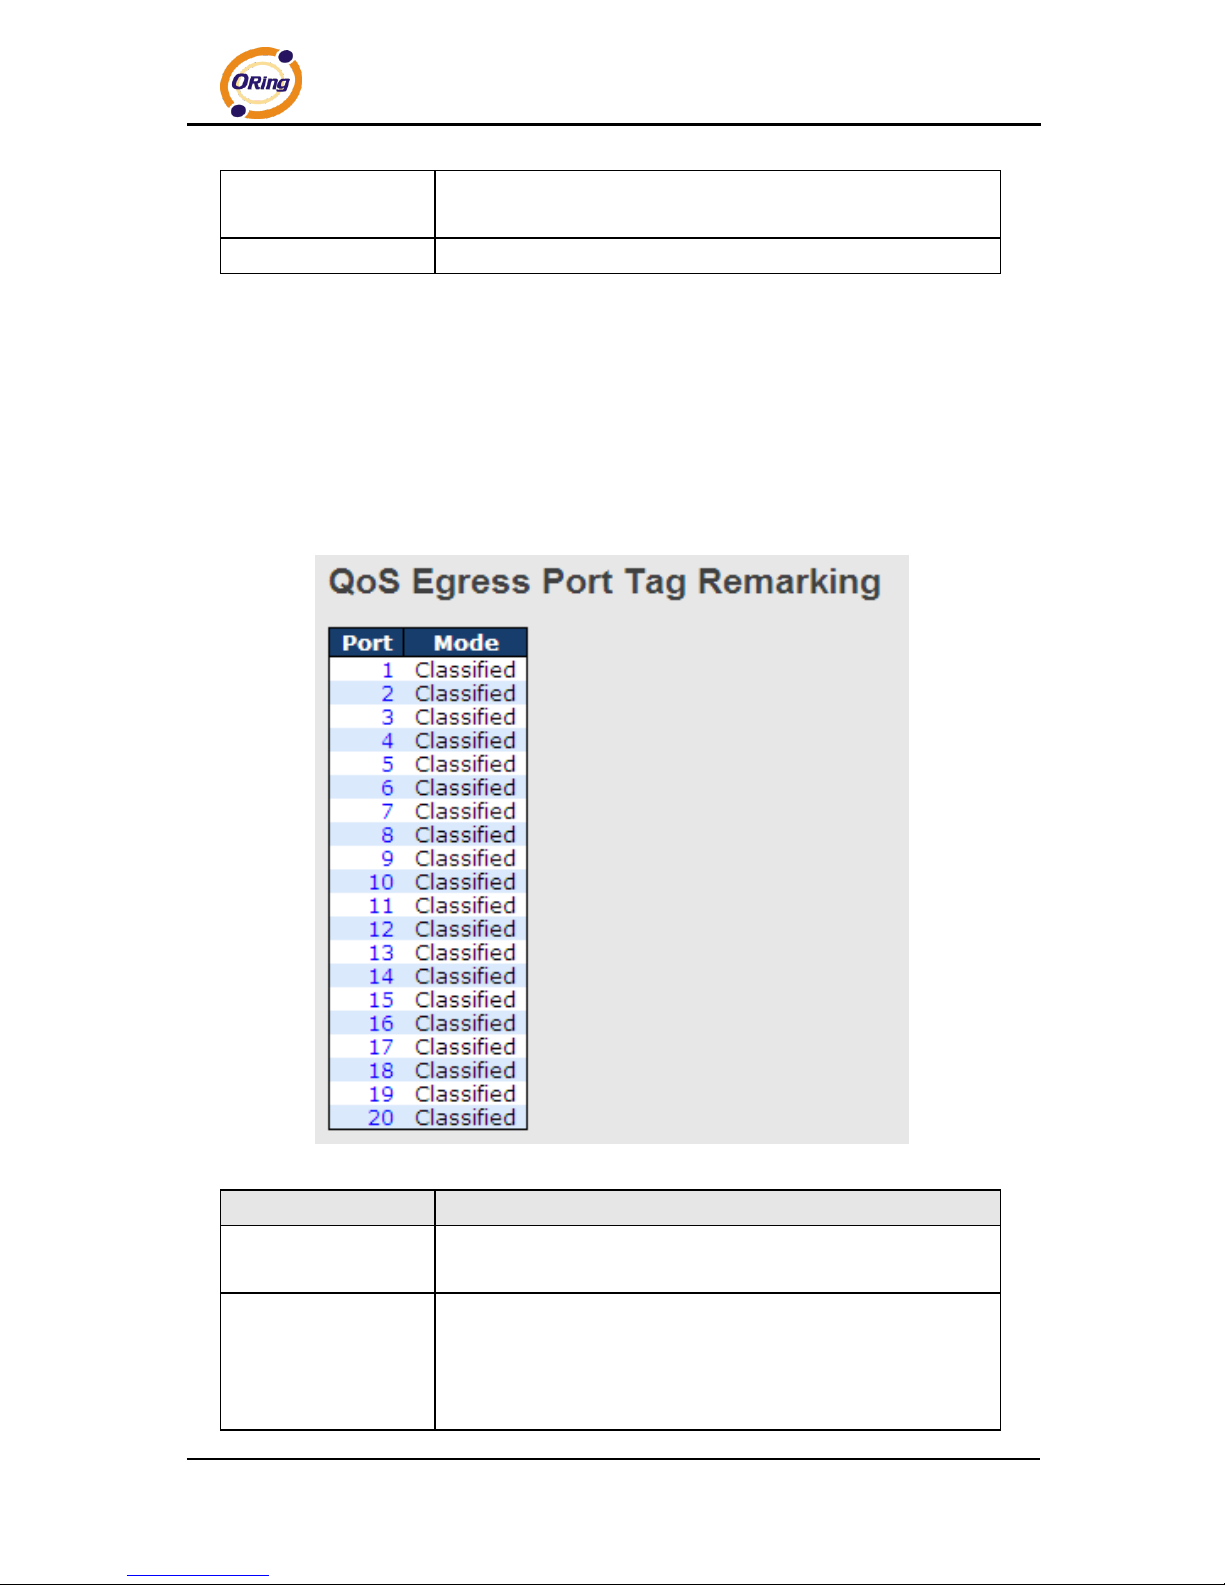
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
77
Tagged frames received on VLAN-unaware ports are always
classified to the default QoS class and DP level.
DSCP Based
Click to enable DSCP-based QoS Ingress Port Classification
5.6.3 Port Tag Remaking
You can set QoS egress queues on a port such as classifying data and marking it according to
its priority and the policies. Packets will then travel across the switch‟s internal paths carrying
their assigned QoS tag markers. At the egress port, these markers are read and used to
determine which queue each data packet is forwarded to. When the traffic does not conform
to the conditions set in a policer command, you can remark the traffic.
Label
Description
Port
The switch port number to which the following settings will be
applied. Click on the port number to configure tag remarking
Mode
Shows the tag remarking mode for this port
Classified: use classified PCP/DEI values
Default: use default PCP/DEI values
Mapped: use mapped versions of QoS class and DP level
Page 79
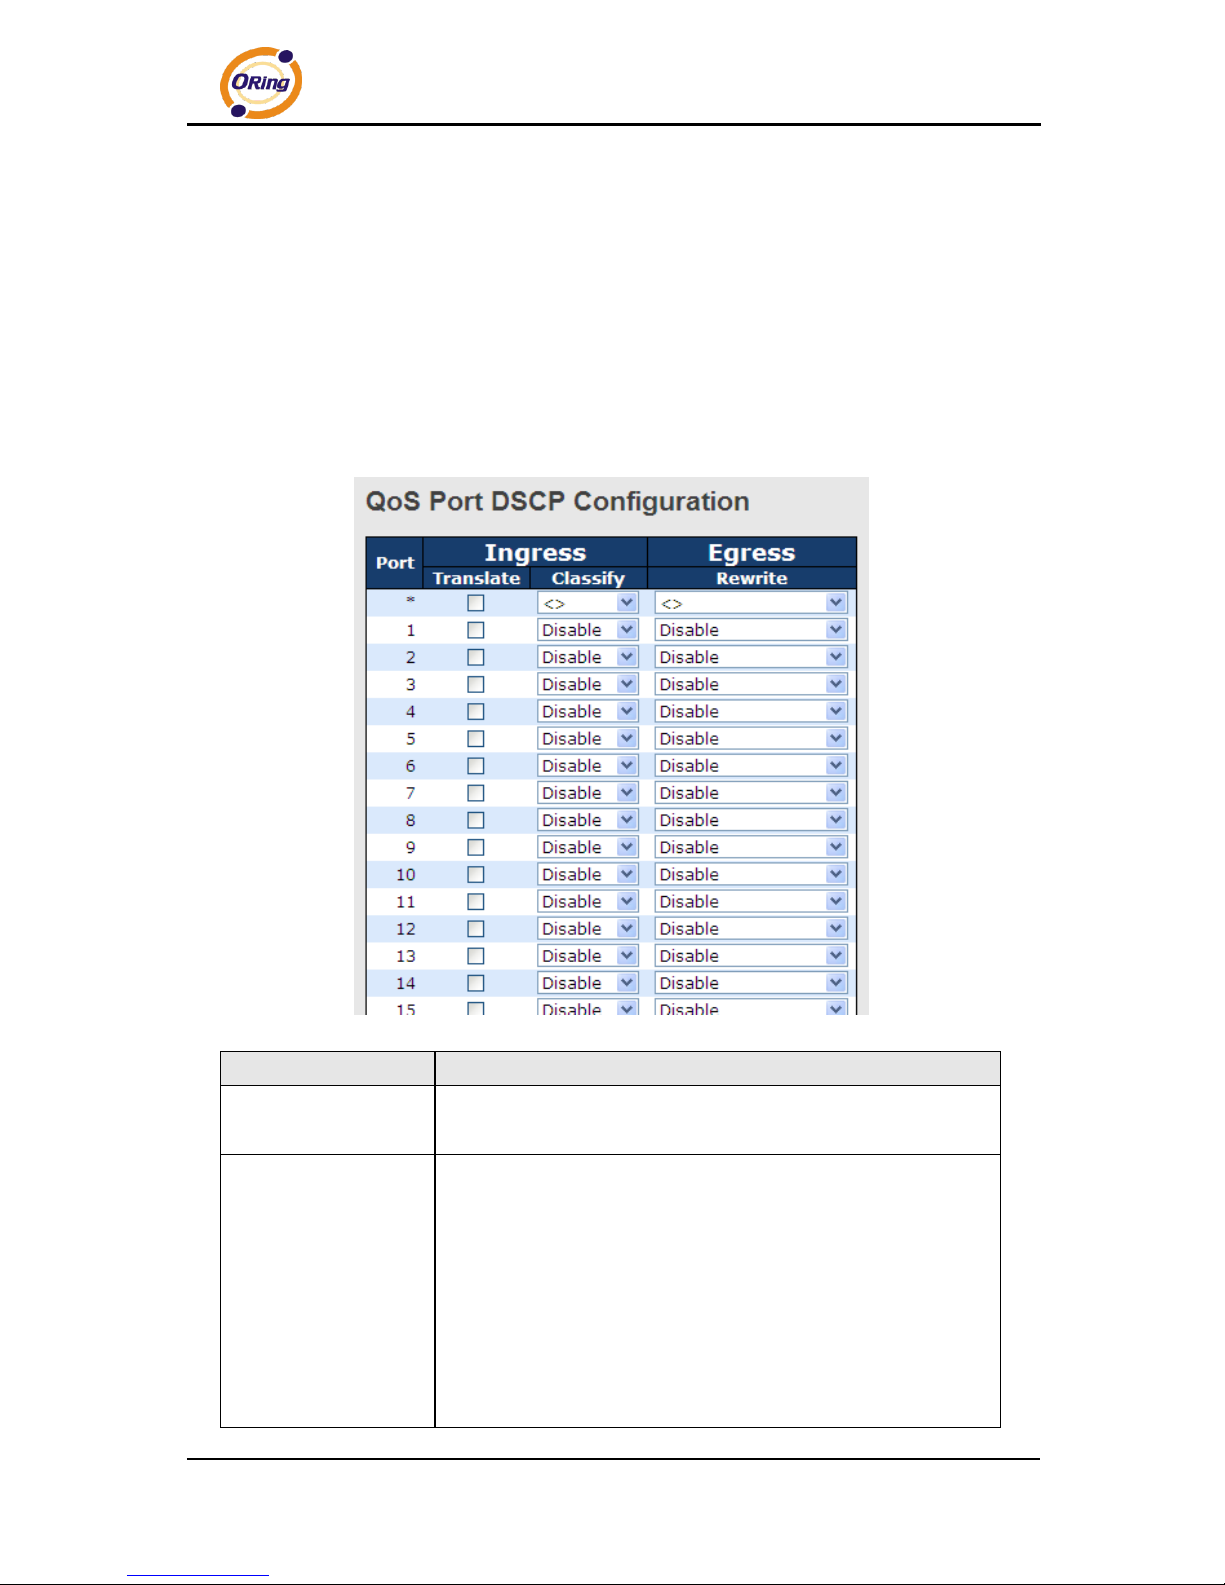
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
78
5.6.4 Port DSCP
DSCP (Differentiated Services Code Point) is a measure of QoS. It can classify data packets
by using the 6-bit DS field in the IP header so you can manage each traffic class differently and
efficiently, thereby achieving optimized use of network bandwidth. DSCP-enabled routers on
the network will read the DSCP value of the data packet and put the packet into different
queues before transmission, such as high priority and most efficient transmission. With such
QoS functions, you can ensure low-latency for critical traffic. This page allows you to configure
DSCP settings for each port.
Label
Description
Port
Shows the list of ports for which you can configure DSCP Ingress
and Egress settings.
Ingress
In Ingress settings you can change ingress translation and
classification settings for individual ports.
There are two configuration parameters available in Ingress:
Translate: check to enable the function
Classify: includes four values
Disable: no Ingress DSCP classification
DSCP=0: classify if incoming (or translated if enabled) DSCP is 0.
Selected: classify only selected DSCP whose classification is
Page 80
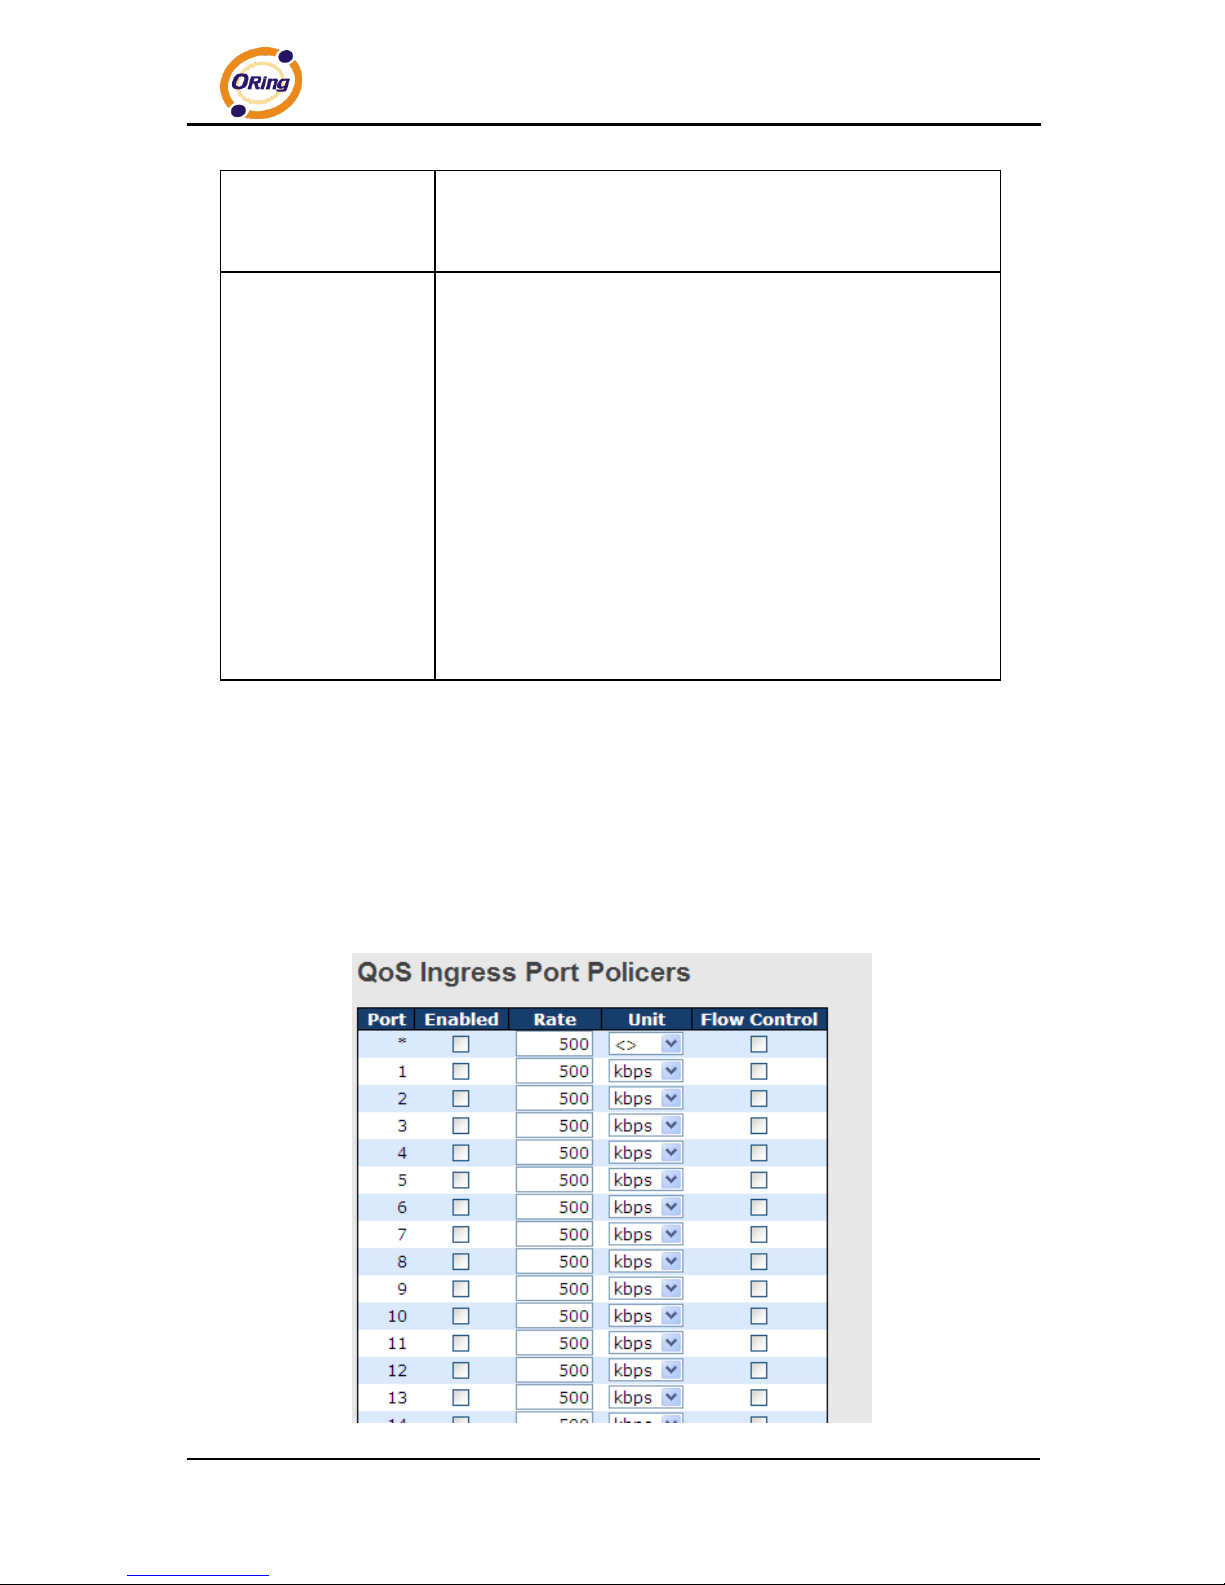
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
79
enabled as specified in DSCP Translation window for the specific
DSCP.
All: classify all DSCP
Egress
Port egress rewriting can be one of the following options:
Disable: no Egress rewrite
Enable: rewrite enabled without remapping
Remap DP Unaware: DSCP from the analyzer is remapped and
the frame is remarked with a remapped DSCP value. The
remapped DSCP value is always taken from the 'DSCP
Translation->Egress Remap DP0' table.
Remap DP Aware: DSCP from the analyzer is remapped and the
frame is remarked with a remapped DSCP value. Depending on
the DP level of the frame, the remapped DSCP value is either
taken from the 'DSCP Translation->Egress Remap DP0' table or
from the 'DSCP Translation->Egress Remap DP1' table.
5.6.5 Policing
Policing is a traffic regulation mechanism for limiting the rate of traffic streams, thereby
controlling the maximum rate of traffic sent or received on an interface. When the traffic rate
exceeds the configured maximum rate, policing drops or remarks the excess traffic. This page
allows you to configure Policer for all switch ports.
Port Policing
Page 81
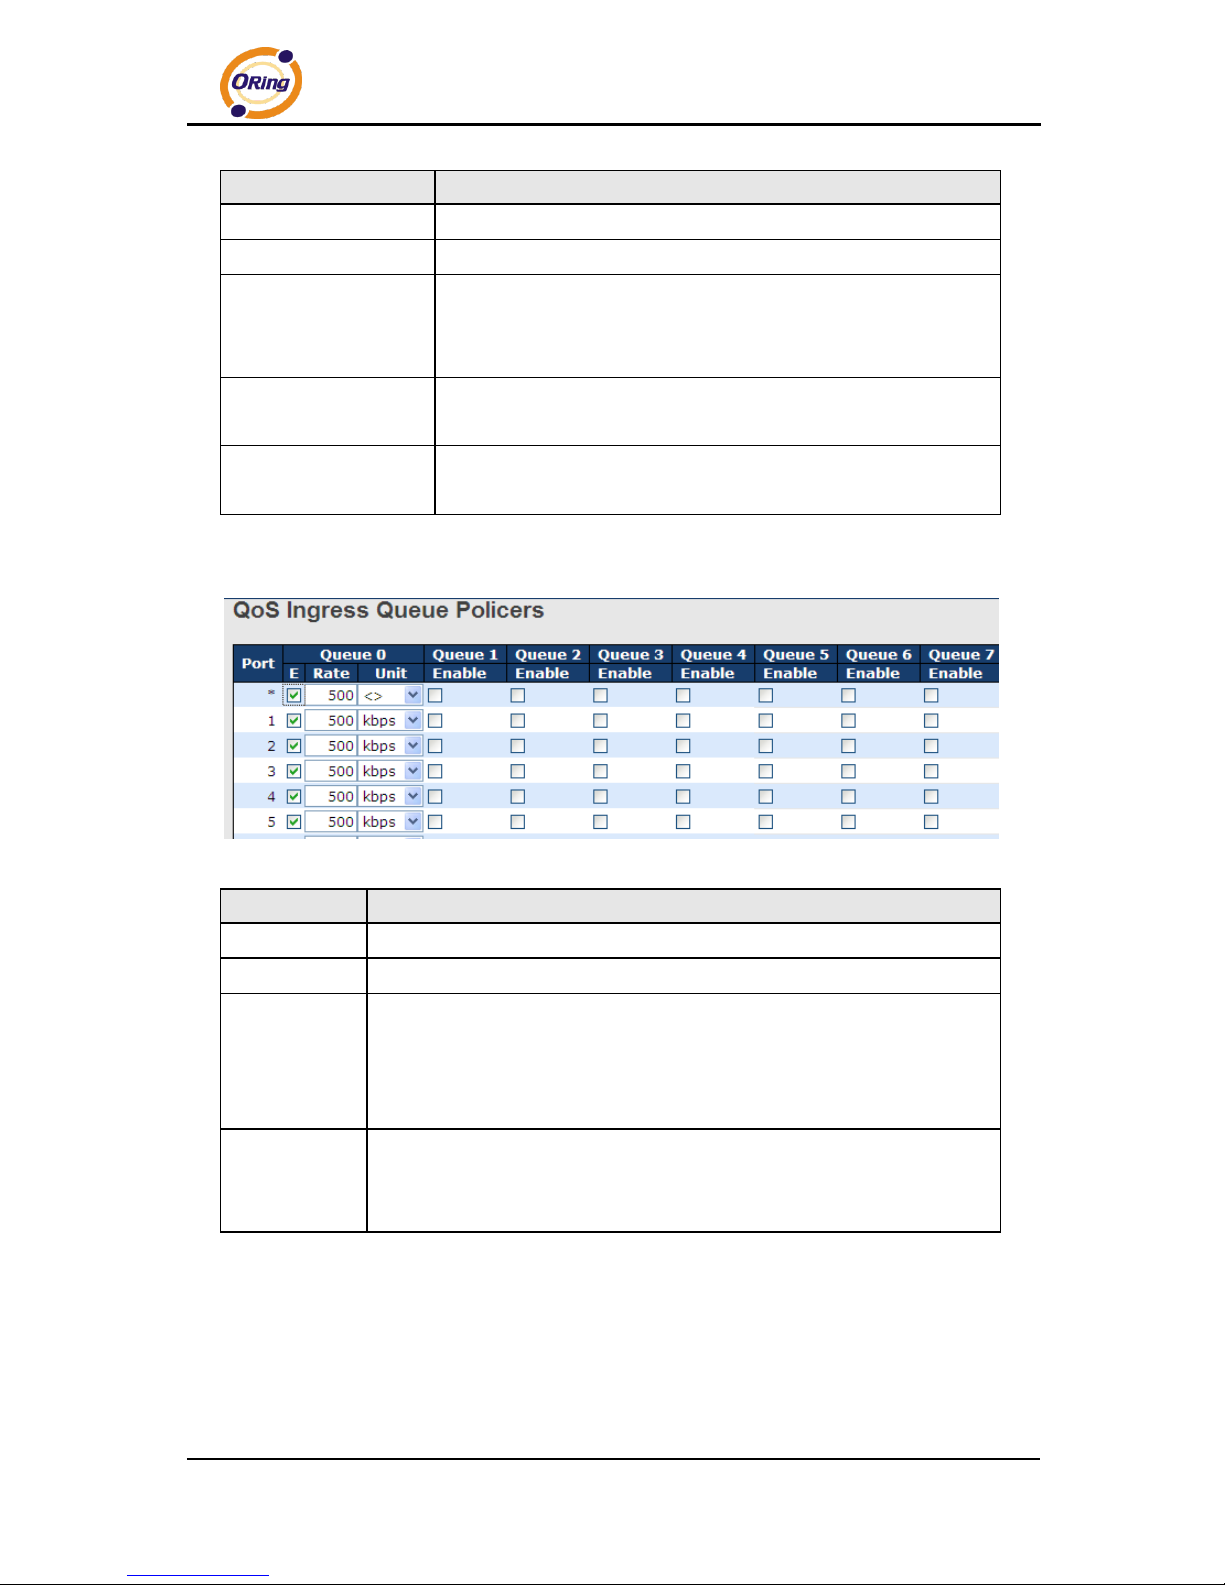
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
80
Label
Description
Port
The port number for which the configuration below applies
Enable
Check to enable the policer for individual switch ports
Rate
Configures the rate of each policer. The default value is 500. This
value is restricted to 100 to 1000000 when the Unit is kbps or
fps, and is restricted to 1 to 3300 when the Unit is Mbps or kfps.
Unti
Configures the unit of measurement for each policer rate as kbps,
Mbps, fps, or kfps. The default value is kbps.
Flow Control
If Flow Control is enabled and the port is in Flow Control mode,
then pause frames are sent instead of being discarded.
Queue Policing
Label
Description
Port
The port number for which the configuration below applies.
Enable(E)
Check to enable queue policer for individual switch ports
Rate
Configures the rate of each queue policer. The default value is 500. This
value is restricted to 100 to 1000000 when the Unit is kbps, and is
restricted to 1 to 3300 when the Unit is Mbps.
This field is only shown if at least one of the queue policers is enabled.
Unit
Configures the unit of measurement for each queue policer rate as kbps
or Mbps. The default value is kbps.
This field is only shown if at least one of the queue policers is enabled.
5.6.6 Scheduling and Shaping
Port scheduling can solve performance degradation during network congestions. The
schedulers allow switches to maintain separate queues for packets from each source and
prevent specific traffic to use up all bandwidth. This page allows you to configure Scheduler
and Shapers for individual ports.
Page 82
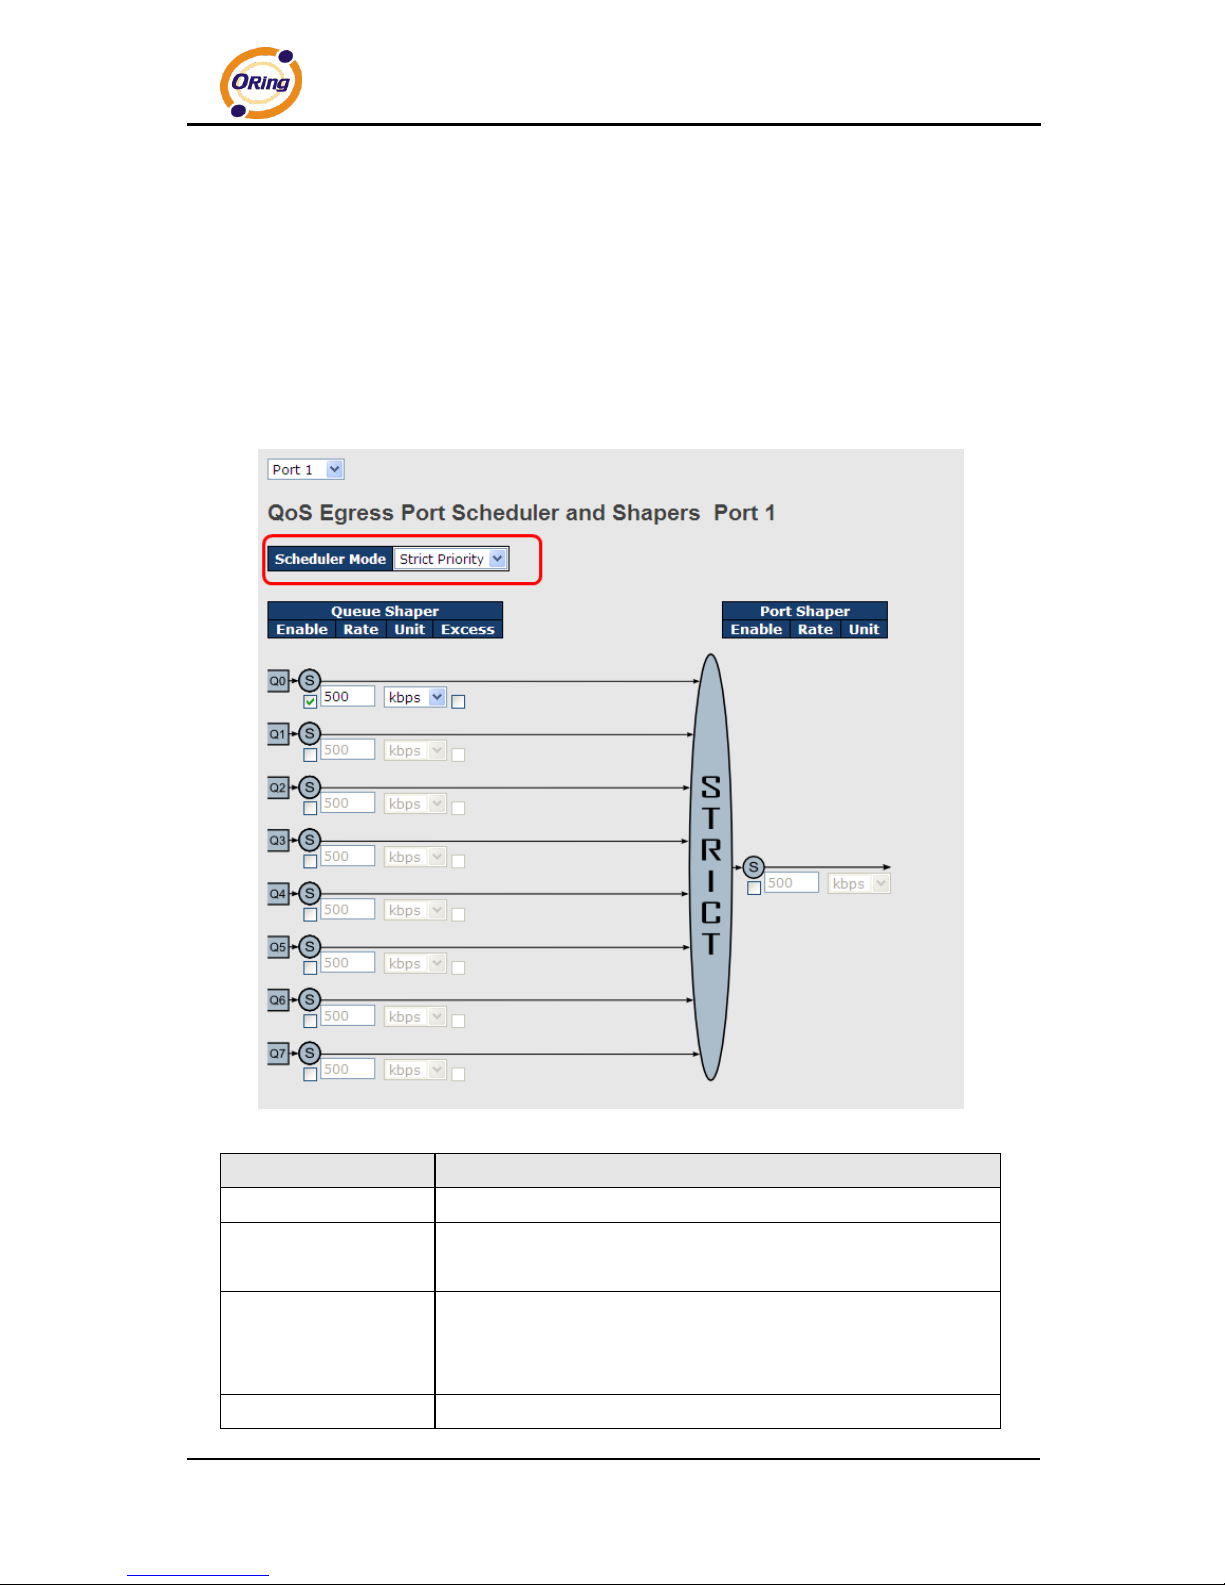
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
81
QoS Egress Port Scheduler and Shaper
Strict Priority
Strict Priority uses queues based only priority. When traffic arrives the device, traffic on the
highest priority queue will be transmitted first, followed by traffic on lower priorities. If there is
always some content in the highest priority queue, then the other packets in the rest of queues
will not be sent until the highest priority queue is empty. The SP algorithm is preferred when
the received packets contain high priority data, such as voice and video.
Label
Description
Scheduler Mode
Two scheduling modes are available: Strict Priority or Weighted
Queue Shaper
Enable
Check to enable queue shaper for individual switch ports
Queue Shaper Rate
Configures the rate of each queue shaper. The default value is
500. This value is restricted to 100 to 1000000 whn the Unit is
kbps", and it is restricted to 1 to 3300 when the Unit is Mbps.
Queues Shaper Unit
Configures the rate for each queue shaper. The default value is
Page 83
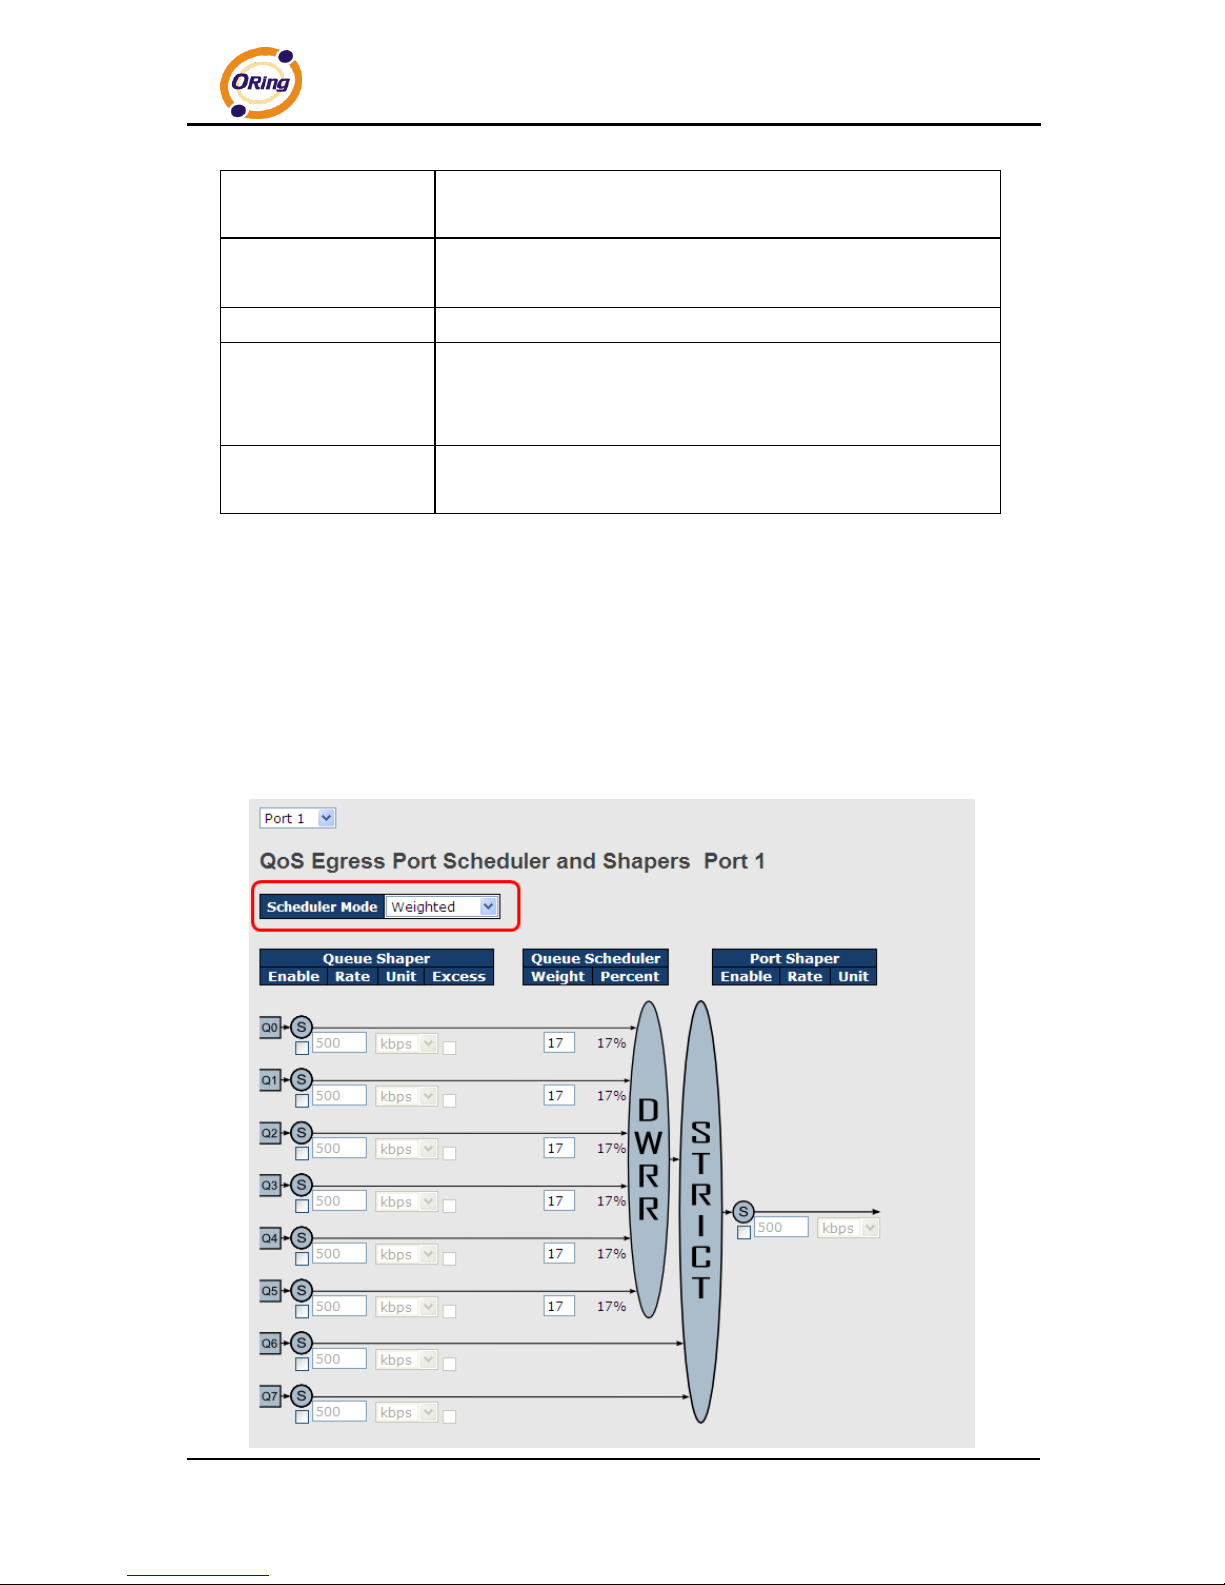
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
82
500. This value is restricted to 100 to 1000000 when the Unit is
kbps, and it is restricted to 1 to 3300 when the Unit is Mbps.
Queue Shaper
Excess
Allows the queue to use excess bandwidth
Port Shaper Enable
Check to enable port shaper for individual switch ports
Port Shaper Rate
Configures the rate of each port shaper. The default value is 500
This value is restricted to 100 to 1000000 when the Unit is kbps,
and it is restricted to 1 to 3300 when the Unit is Mbps.
Port Shaper Unit
Configures the unit of measurement for each port shaper rate as
kbps or Mbps. The default value is kbps.
Weighted
Weighted scheduling will deliver traffic on a rotating basis. It can guarantee each queue‟s
minimum bandwidth based on their bandwidth weight when there is traffic congestion. Only
when a port has more traffic than it can handle will this mode be activated. A queue is given an
amount of bandwidth regardless of the incoming traffic on that port. Queue with larger weights
will have more guaranteed bandwidth than others with smaller weights.
Page 84
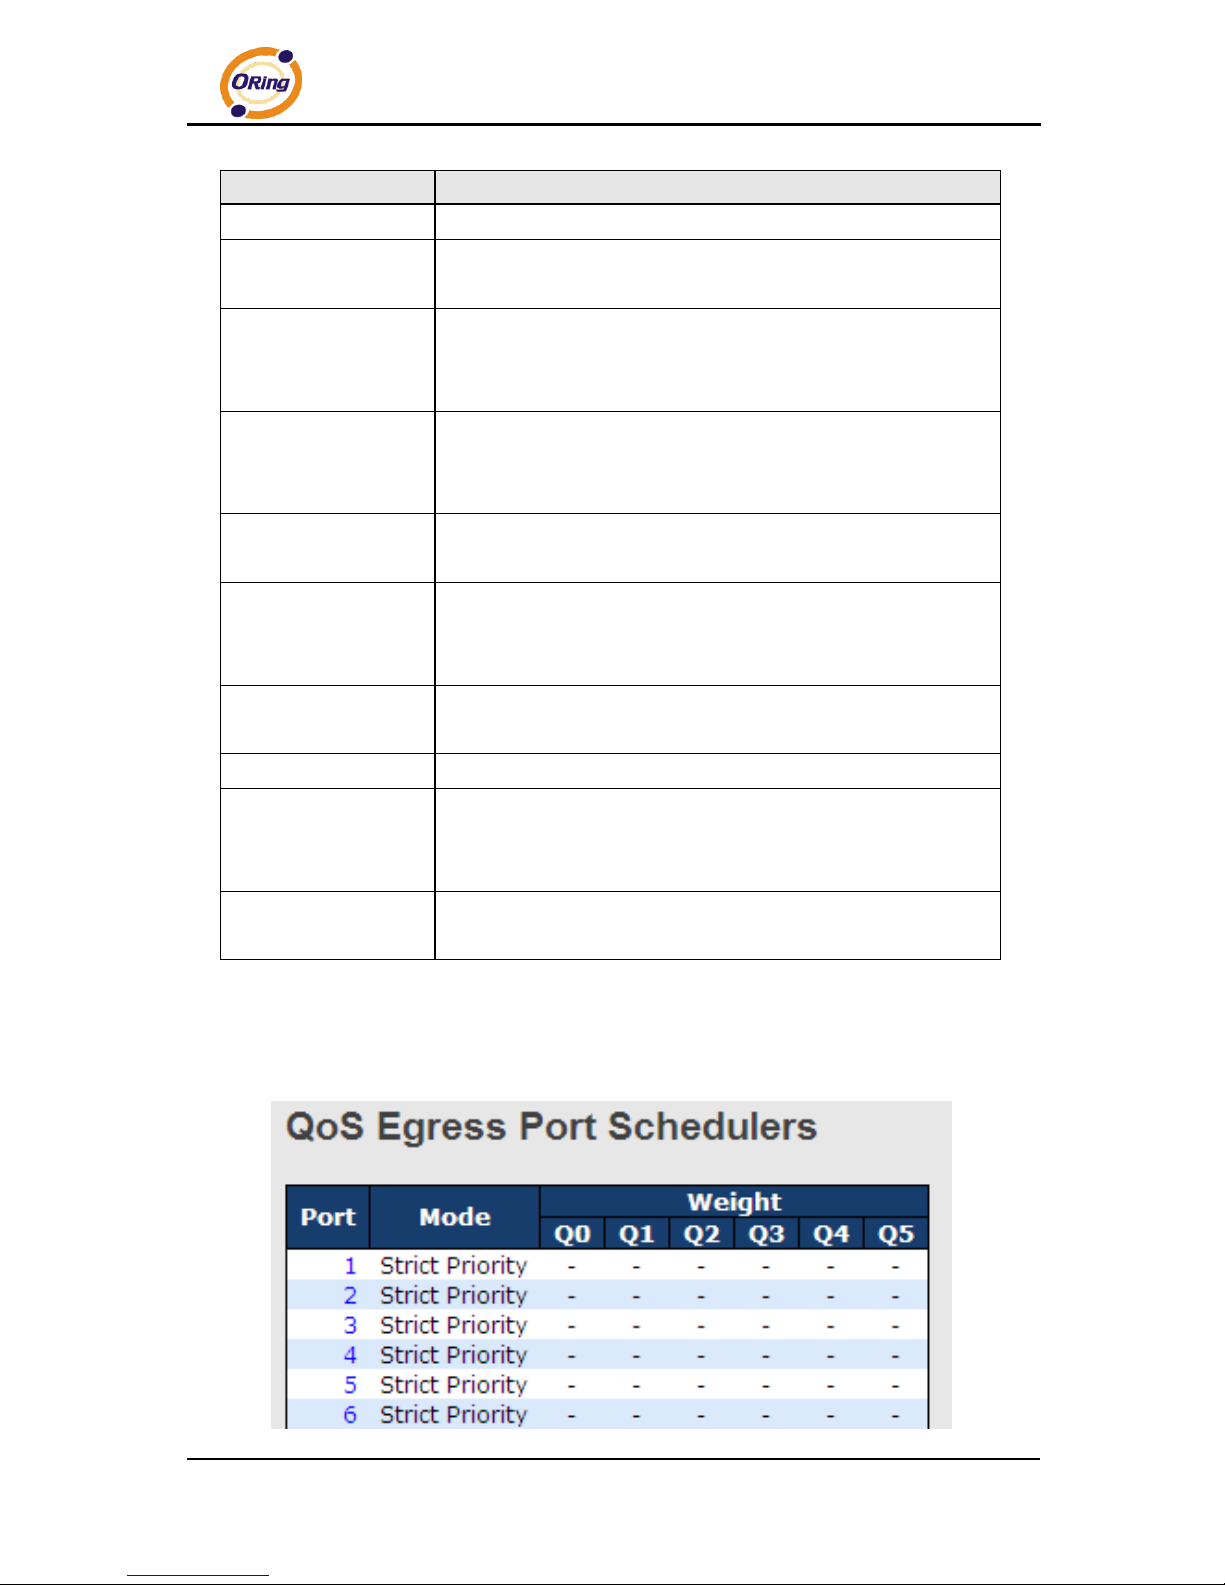
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
83
Label
Description
Scheduler Mode
Two scheduling modes are available: Strict Priority or Weighted
Queue Shaper
Enable
Check to enable queue shaper for individual switch ports
Queue Shaper Rate
Configures the rate of each queue shaper. The default value is
500. This value is restricted to 100 to 1000000 when the Unit is
kbps, and it is restricted to 1 to 3300 when the Unit is Mbps.
Queues Shaper Unit
Configures the rate of each queue shaper. The default value is
500. This value is restricted to 100 to 1000000 when the Unit" is
kbps, and it is restricted to 1 to 3300 when the Unit is Mbps.
Queue Shaper
Excess
Allows the queue to use excess bandwidth
Queue Scheduler
Weight
Configures the weight of each queue. The default value is 17.
This value is restricted to 1 to 100. This parameter is only shown if
Scheduler Mode is set to Weighted.
Queue Scheduler
Percent
Shows the weight of the queue in percentage. This parameter is
only shown if Scheduler Mode is set to Weighted.
Port Shaper Enable
Check to enable port shaper for individual switch ports
Port Shaper Rate
Configures the rate of each port shaper. The default value is 500.
This value is restricted to 100 to 1000000 when the Unit is kbps,
and it is restricted to 1 to 3300 when the Unit is Mbps.
Port Shaper Unit
Configures the unit of measurement for each port shaper rate as
kbps or Mbps. The default value is kbps.
5.6.7 Port Scheduler
This page provides an overview of QoS Egress Port Schedulers for all switch ports.
Page 85
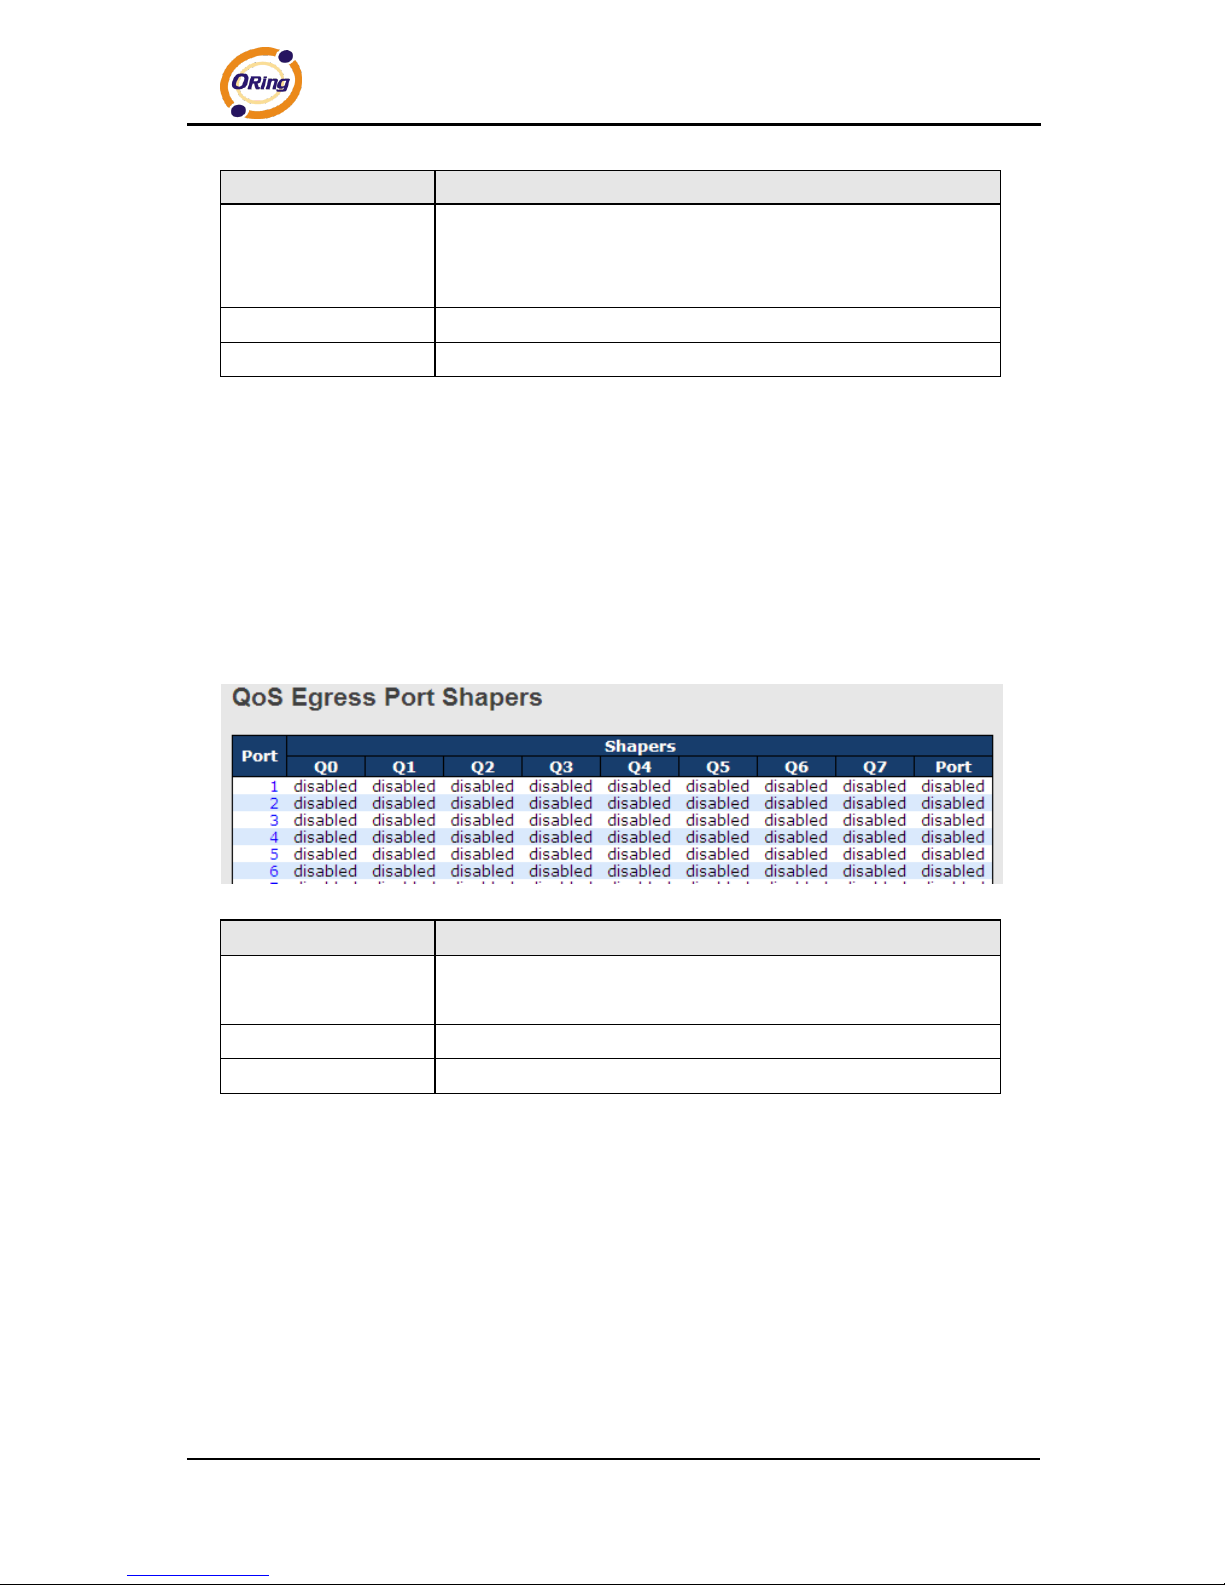
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
84
Label
Description
Port
The switch port number to which the following settings will be
applied.
Click on the port number to configure the schedulers
Mode
Shows the scheduling mode for this port
Qn
Shows the weight for this queue and port
5.6.8 Port Shaping
Port shaping enables you to limit traffic on a port, thereby controlling the amount of traffic
passing through the port. With port shaping, you can shape the aggregate traffic through an
interface to a rate that is less than the line rate for that interface. When configuring port
shaping on an interface, you specify a value indicating the maximum amount of traffic
allowable for the interface. This value must be less than the maximum bandwidth for that
interface.
Label
Description
Port
The switch port number to which the following settings will be
applied. Click on the port number to configure the shapers
Mode
Shows disabled or actual queue shaper rate - e.g. "800 Mbps"
Q0~Q7
Shows disabled or actual port shaper rate - e.g. "800 Mbps"
5.6.9 DSCP-based QoS
This page allows you to configure DSCP-based QoS Ingress Classification settings for all
ports.
Page 86
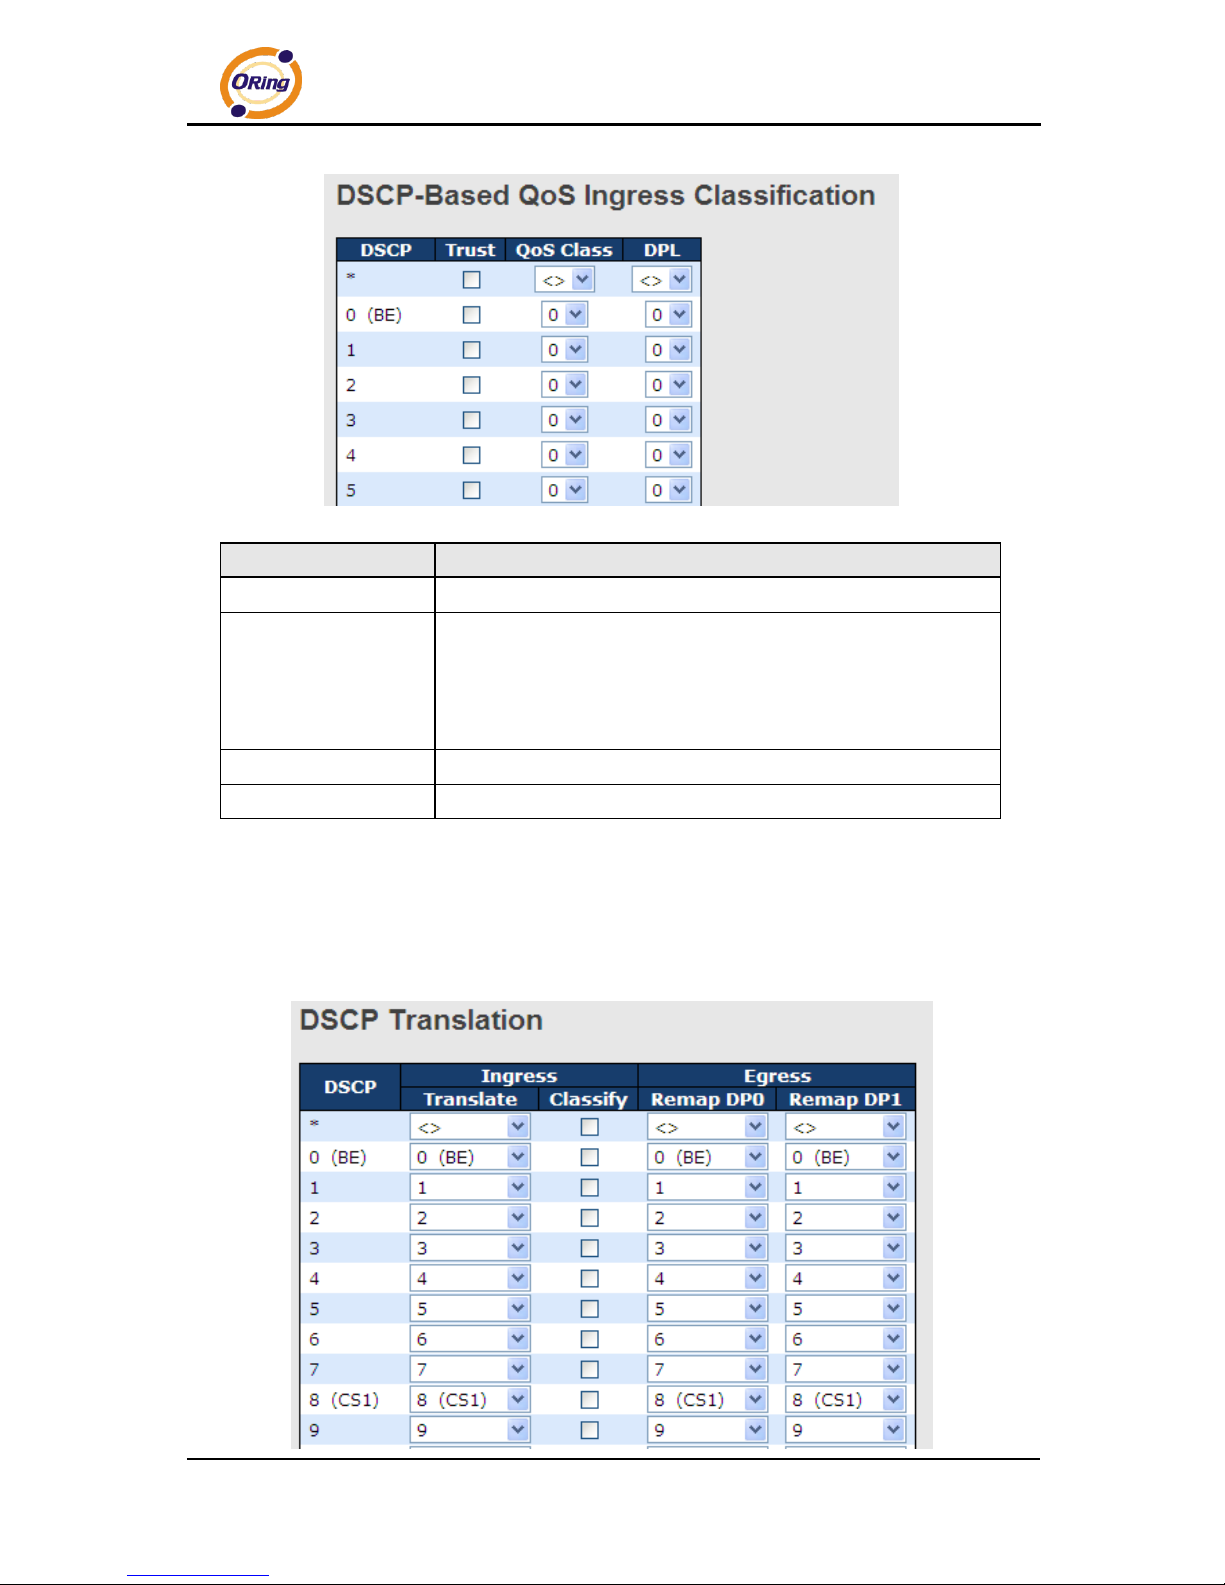
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
85
Label
Description
DSCP
Maximum number of supported DSCP values is 64
Trust
Check to trust a specific DSCP value. Only frames with trusted
DSCP values are mapped to a specific QoS class and drop
precedence level. Frames with untrusted DSCP values are
treated as a non-IP frame.
QoS Class
QoS class value can be any number from 0-7.
DPL
Drop Precedence Level (0-1)
5.6.10 DSCP Translation
This page allows you to configure basic QoS DSCP translation settings for all switches. DSCP
translation can apply to Ingress or Egress.
Page 87
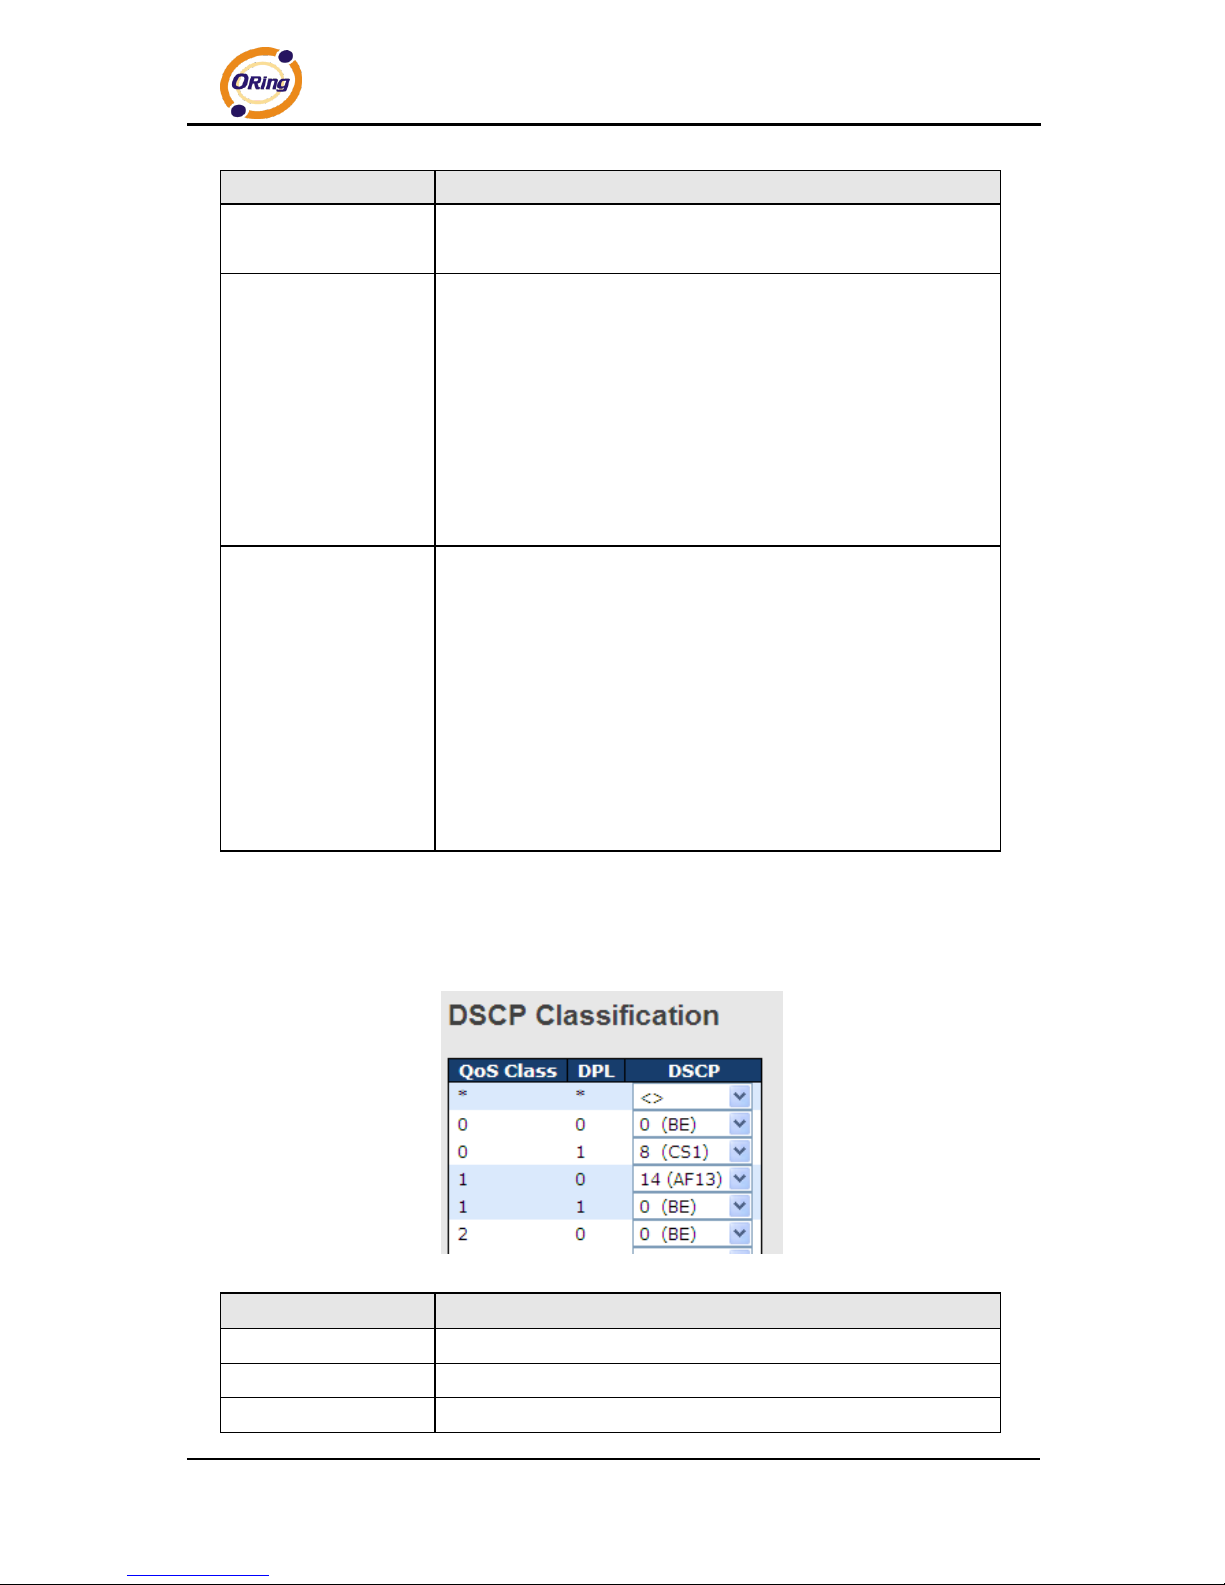
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
86
Label
Description
DSCP
Maximum number of supported DSCP values is 64 and valid
DSCP value ranges from 0 to 63.
Ingress
Ingress DSCP can be first translated to new DSCP before using
the DSCP for QoS class and DPL map.
There are two configuration parameters for DSCP Translation -
1. Translate: Enables ingress translation of DSCP values based
on the specified classification method. DSCP can be translated to
any of (0-63) DSCP values.
2. Classify: Enable Classification at ingress side as defined in the
QoS Port DSCP Configuration table.
Egress
Configurable engress parameters include;
Remap DP0: Re-maps DP0 field to selected DSCP value. DP0
indicates a drop precedence with a low priority. You can select the
DSCP value from a selected menu to which you want to remap.
DSCP value ranges form 0 to 63.
Remap DP1: Re-maps DP1 field to selected DSCP value. DP1
indicates a drop precedence with a high priority. You can select
the DSCP value from a selected menu to which you want to
remap. DSCP value ranges form 0 to 63.
5.6.11 DSCP Classification
This page allows you to configure the mapping of QoS class and Drop Precedence Level to
DSCP value.
Label
Description
QoS Class
Actual QoS class
DPL
Actual Drop Precedence Level
DSCP
Select the classified DSCP value (0-63)
Page 88
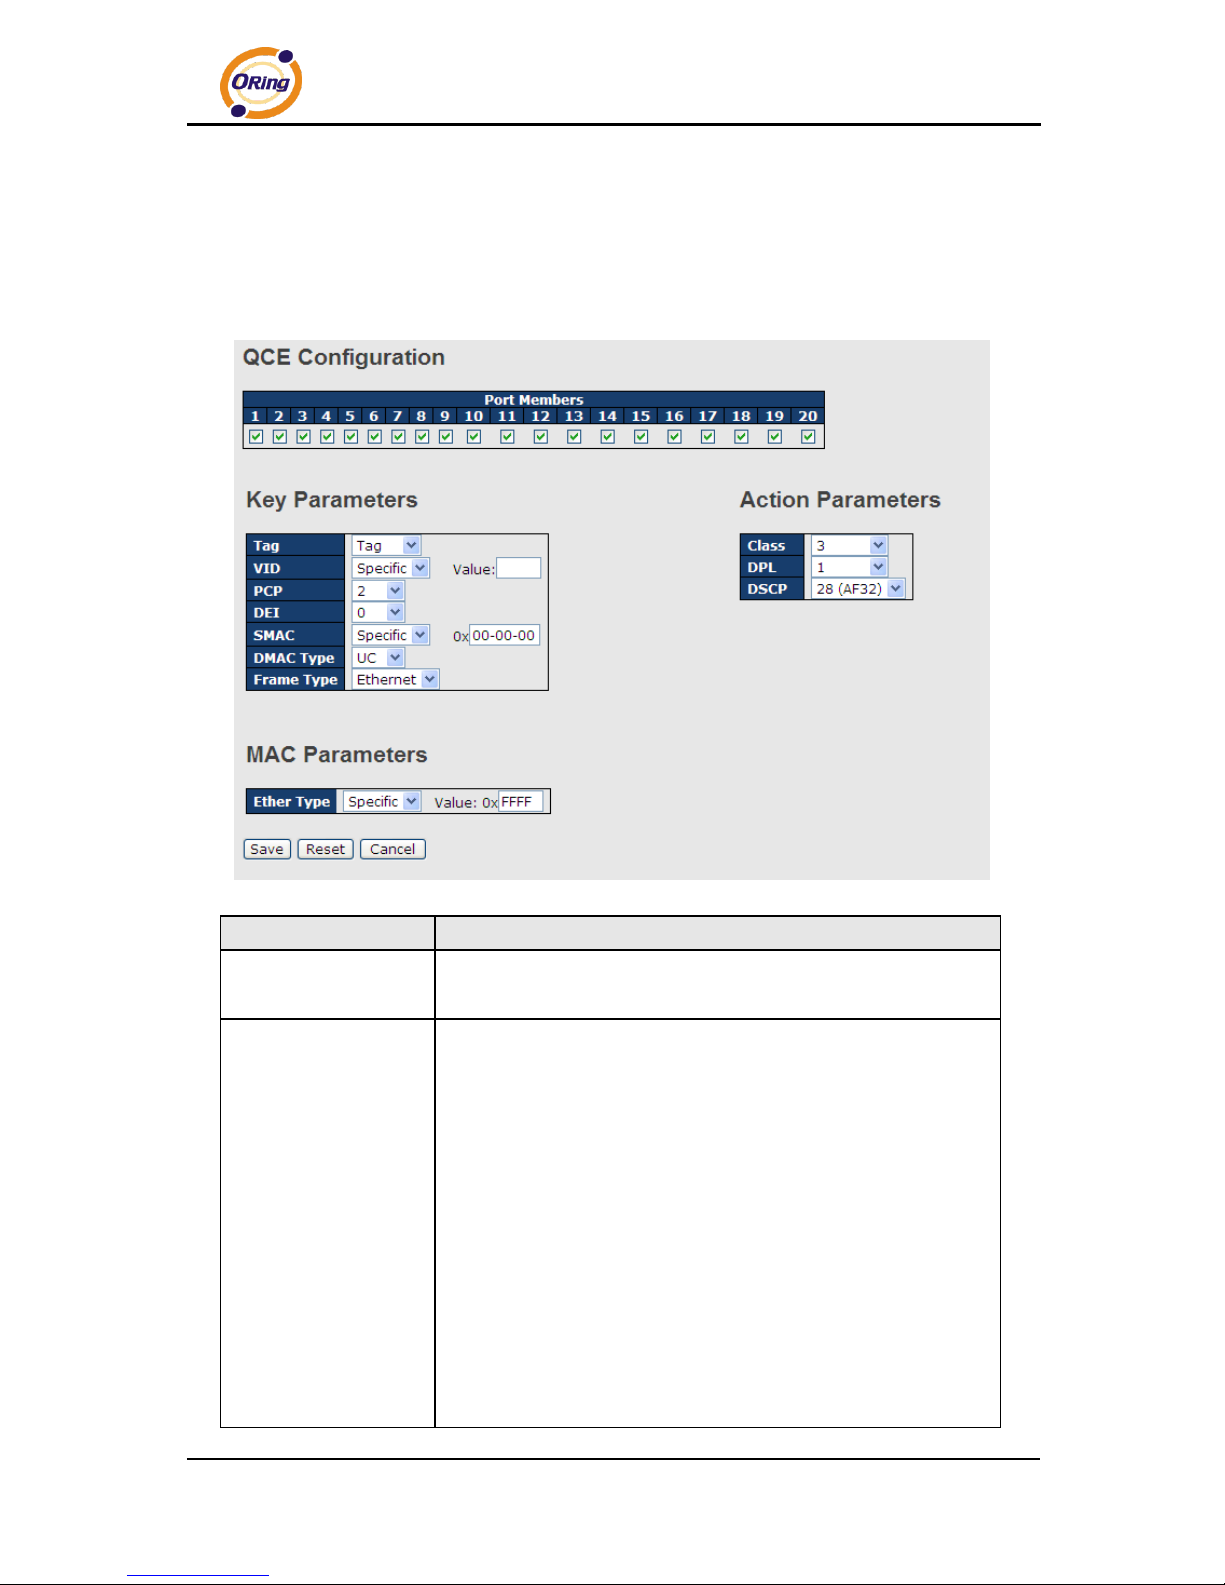
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
87
5.6.12 QoS Control List
This page shows all the QCE (Quality Control Entries) for a given QCL. You can edit or add
new QoS control entries in this page. A QCE consists of several parameters. These
parameters vary with the frame type you select.
Label
Description
Port Members
Check to include the port in the QCL entry. By default, all ports are
included.
Key Parameters
Key configurations include:
Tag: value of tag, can be Any, Untag or Tag.
VID: valid value of VLAN ID from 1 to 4095
Any: can be a specific value or a range of VIDs.
PCP: Priority Code Point, can be specific numbers (0, 1, 2, 3, 4, 5,
6, 7), a range (0-1, 2-3, 4-5, 6-7, 0-3, 4-7) or Any
DEI: Drop Eligible Indicator, can be any of values between 0 and
1 or Any
SMAC: Source MAC Address, can be 24 MS bits (OUI) or Any
DMAC Type: Destination MAC type, can be unicast (UC),
multicast (MC), broadcast (BC) or Any
Frame Type can be the following values: Any, Ethernet, LLC,
Page 89
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
88
SNAP, IPv4, and IPv6
Note: all frame types are explained below.
Any
Allow all types of frames
Ethernet
Valid Ethernet values can range from 0x600 to 0xFFFF or Any' but
excluding 0x800(IPv4) and 0x86DD(IPv6). The default value is
Any.
LLC
SSAP Address: valid SSAP (Source Service Access Point) values
can range from 0x00 to 0xFF or Any. The default value is Any.
DSAP Address: valid DSAP (Destination Service Access Point)
values can range from 0x00 to 0xFF or Any. The default value is
Any.
Control Valid Control: valid values can range from 0x00 to 0xFF or
Any. The default value is Any.
SNAP
PID: valid PID (a.k.a ethernet type) values can range from 0x00 to
0xFFFF or Any. The default value is Any.
IPv4
Protocol IP Protocol Number: (0-255, TCP or UDP) or Any
Source IP: specific Source IP address in value/mask format or
Any. IP and mask are in the format of x.y.z.w where x, y, z, and w
are decimal numbers between 0 and 255. When the mask is
converted to a 32-bit binary string and read from left to right, all
bits following the first zero must also be zero.
DSCP (Differentiated Code Point): can be a specific value, a
range, or Any. DSCP values are in the range 0-63 including BE,
CS1-CS7, EF or AF11-AF43.
IP Fragment: Ipv4 frame fragmented options include 'yes', 'no',
and 'any'.
Sport Source TCP/UDP Port: (0-65535) or Any, specific value or
port range applicable for IP protocol UDP/TCP
Dport Destination TCP/UDP Port: (0-65535) or Any, specific
value or port range applicable for IP protocol UDP/TCP
IPv6
Protocol IP protocol number: (0-255, TCP or UDP) or Any
Source IP IPv6 source address: (a.b.c.d) or Any, 32 LS bits
DSCP (Differentiated Code Point): can be a specific value, a
range, or Any. DSCP values are in the range 0-63 including BE,
CS1-CS7, EF or AF11-AF43.
Sport Source TCP/UDP port: (0-65535) or Any, specific value or
port range applicable for IP protocol UDP/TCP
Page 90
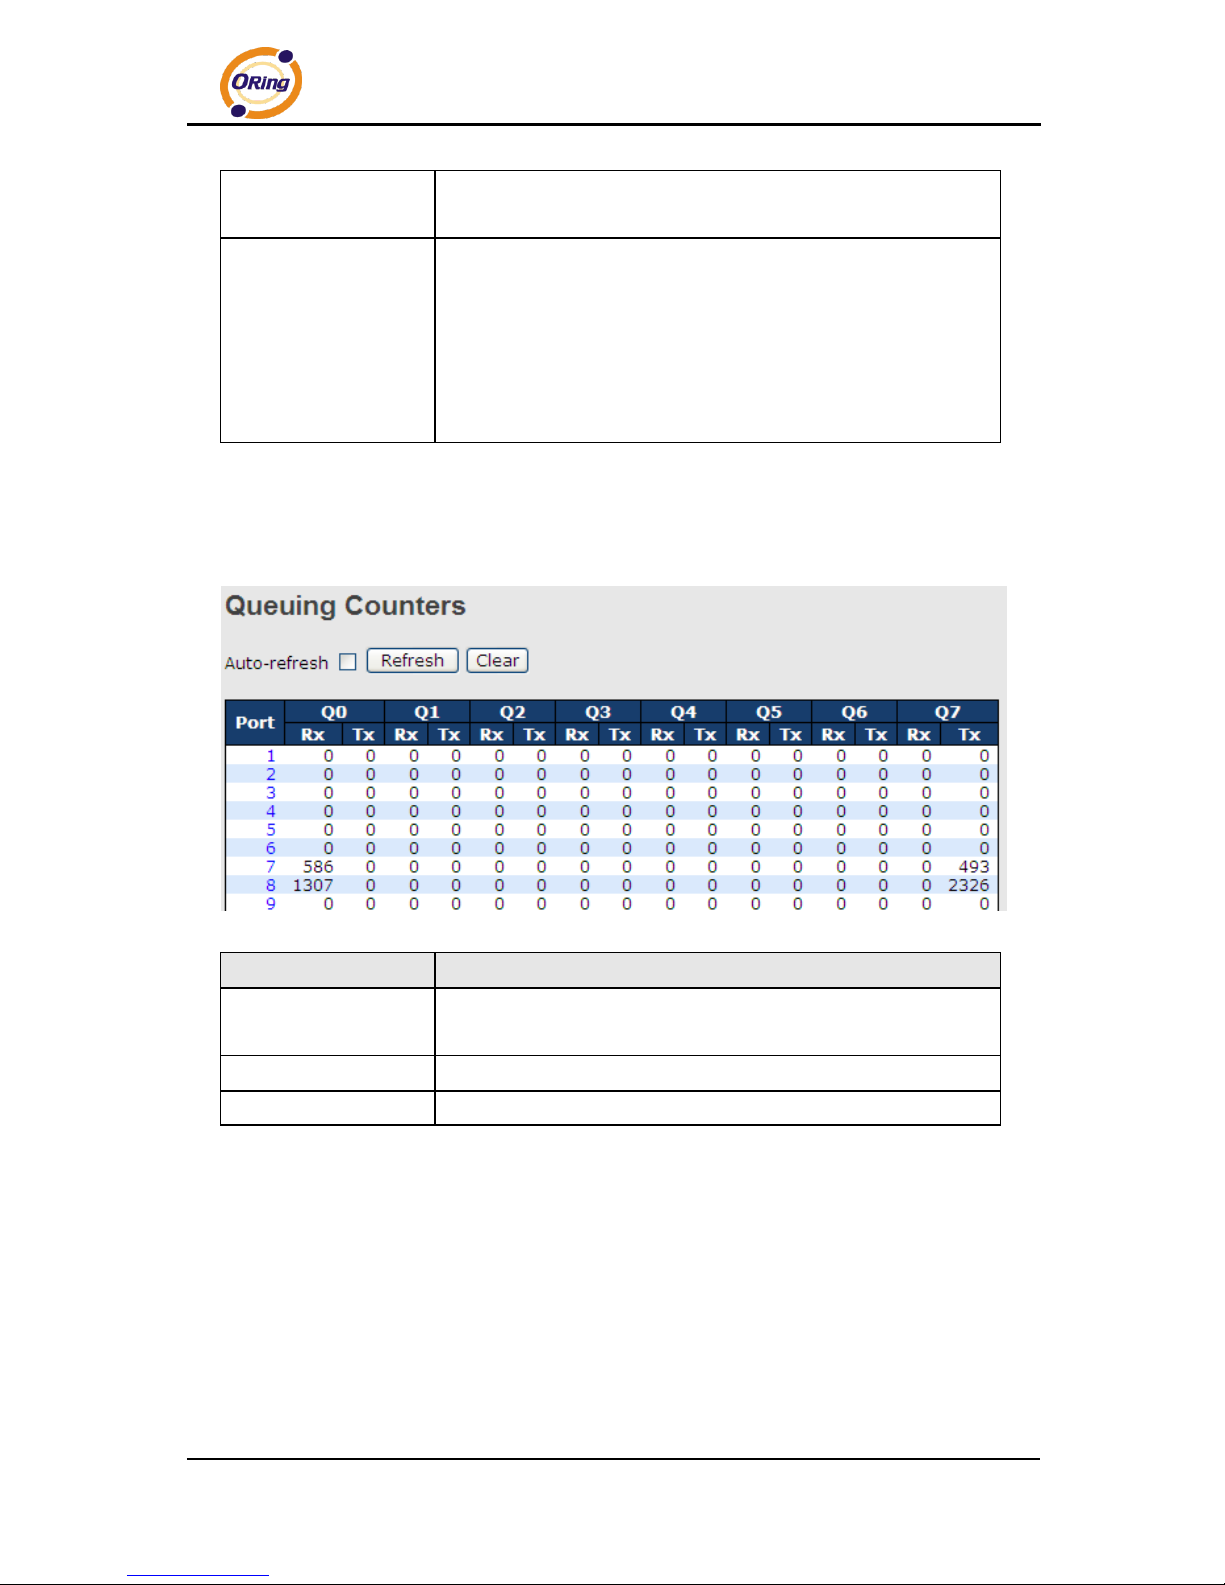
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
89
Dport Destination TCP/UDP port: (0-65535) or Any, specific value
or port range applicable for IP protocol UDP/TCP
Action Parameters
Class QoS class: (0-7) or Default
Valid Drop Precedence Level value can be (0-1) or Default.
Valid DSCP value can be (0-63, BE, CS1-CS7, EF or AF11-AF43)
or Default.
Default means that the default classified value is not modified by
this QCE.
5.6.13 QoS Counters
This page shows information on the number of packets sent and received at each queue.
Label
Description
Port
The switch port number to which the following settings will be
applied.
Qn
There are 8 QoS queues per port. Q0 is the lowest priority
Rx / Tx
The number of received and transmitted packets per queue
5.6.14 QCL Status
This page shows the QCL status by different QCL users. Each row describes the QCE that is
defined. A conflict will occur if a specific QCE is not applied to the hardware due to hardware
limitations. The maximum number of QCEs is 256 on each switch.
Page 91
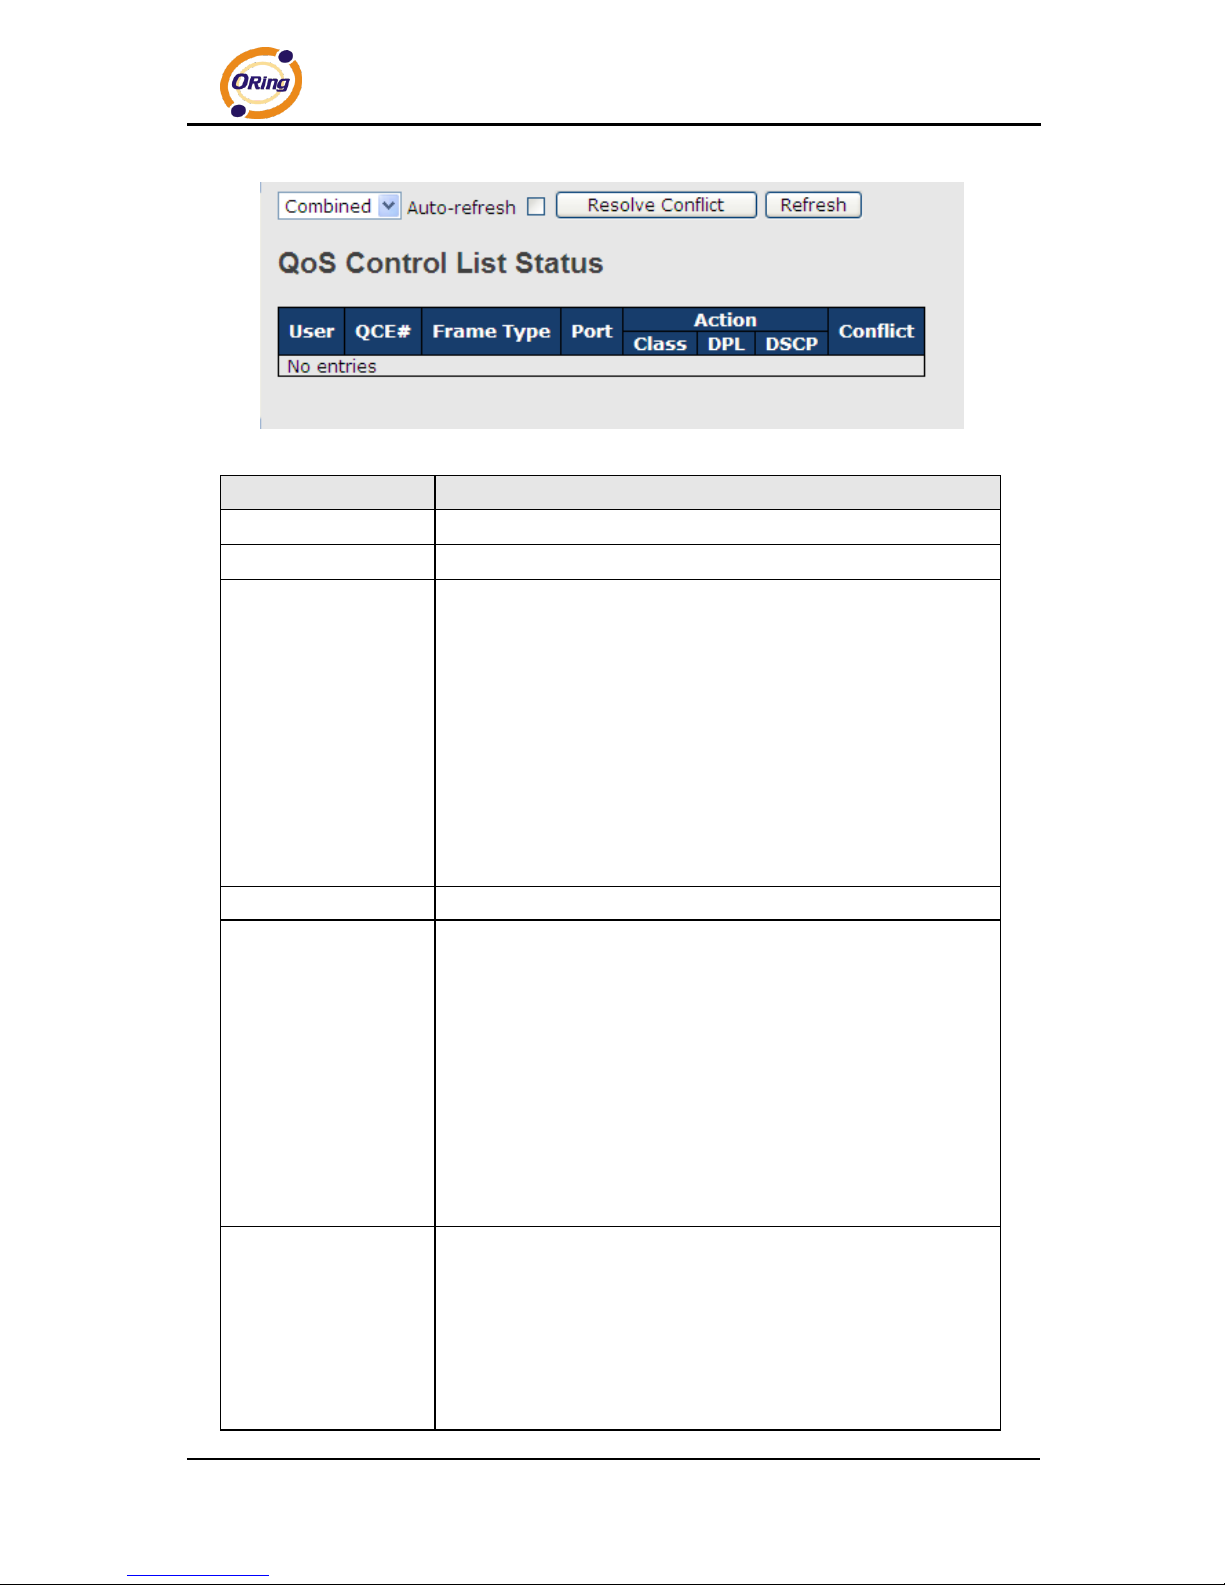
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
90
Label
Description
User
Indicates the QCL user
QCE#
Indicates the index of QCE
Frame Type
Indicates the type of frame to look for incoming frames. Possible
frame types are:
Any: the QCE will match all frame type.
Ethernet: Only Ethernet frames (with Ether Type 0x600-0xFFFF)
are allowed.
LLC: Only (LLC) frames are allowed.
SNAP: Only (SNAP) frames are allowed.
IPv4: the QCE will match only IPV4 frames.
IPv6: the QCE will match only IPV6 frames.
Port
Indicates the list of ports configured with the QCE.
Action
Indicates the classification action taken on ingress frame if
parameters configured are matched with the frame's content.
There are three action fields: Class, DPL, and DSCP.
Class: Classified QoS; if a frame matches the QCE, it will be put
in the queue.
DPL: Drop Precedence Level; if a frame matches the QCE, then
DP level will set to a value displayed under DPL column.
DSCP: if a frame matches the QCE, then DSCP will be classified
with the value displayed under DSCP column.
Conflict
Displays the conflict status of QCL entries. As hardware
resources are shared by multiple applications, resources required
to add a QCE may not be available. In that case, it shows conflict
status as Yes, otherwise it is always No. Please note that conflict
can be resolved by releasing the hardware resources required to
add the QCL entry by pressing Resolve Conflict button.
Page 92
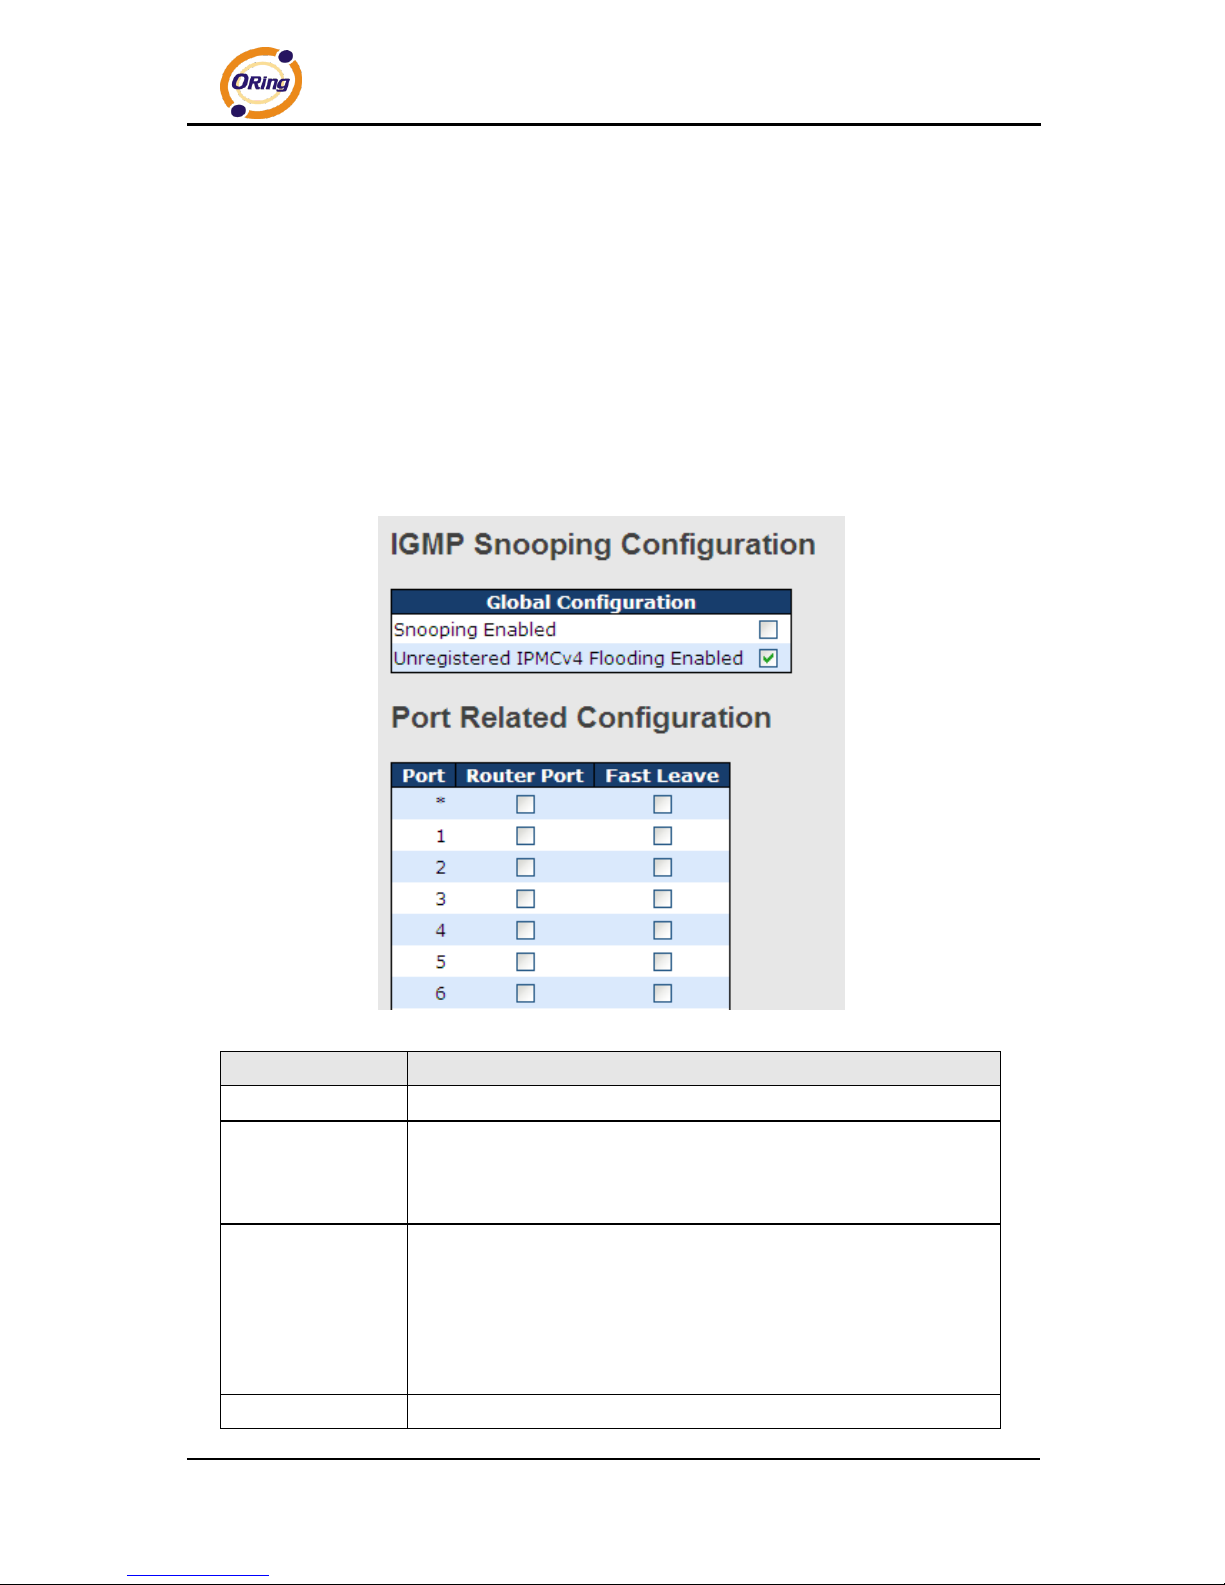
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
91
5.7 Multicast
5.7.1 IGMP Snooping
IGMP (Internet Group Management Protocol) snooping monitors the IGMP traffic between
hosts and multicast routers. The switch uses what IGMP snooping learns to forward multicast
traffic only to interfaces that are connected to interested receivers. This conserves bandwidth
by allowing the switch to send multicast traffic to only those interfaces that are connected to
hosts that want to receive the traffic, instead of flooding the traffic to all interfaces in the VLAN.
This page allows you to set up IGMP snooping configurations.
Label
Description
Snooping Enabled
Check to enable global IGMP snooping
Unregistered
IPMCv4Flooding
enabled
Check to enable unregistered IPMC traffic flooding
Router Port
Specifies which ports act as router ports. A router port is a port on the
Ethernet switch that leads towards the Layer 3 multicast device or
IGMP querier.
If an aggregation member port is selected as a router port, the whole
aggregation will act as a router port.
Fast Leave
Check to enable fast leave on the port
Page 93
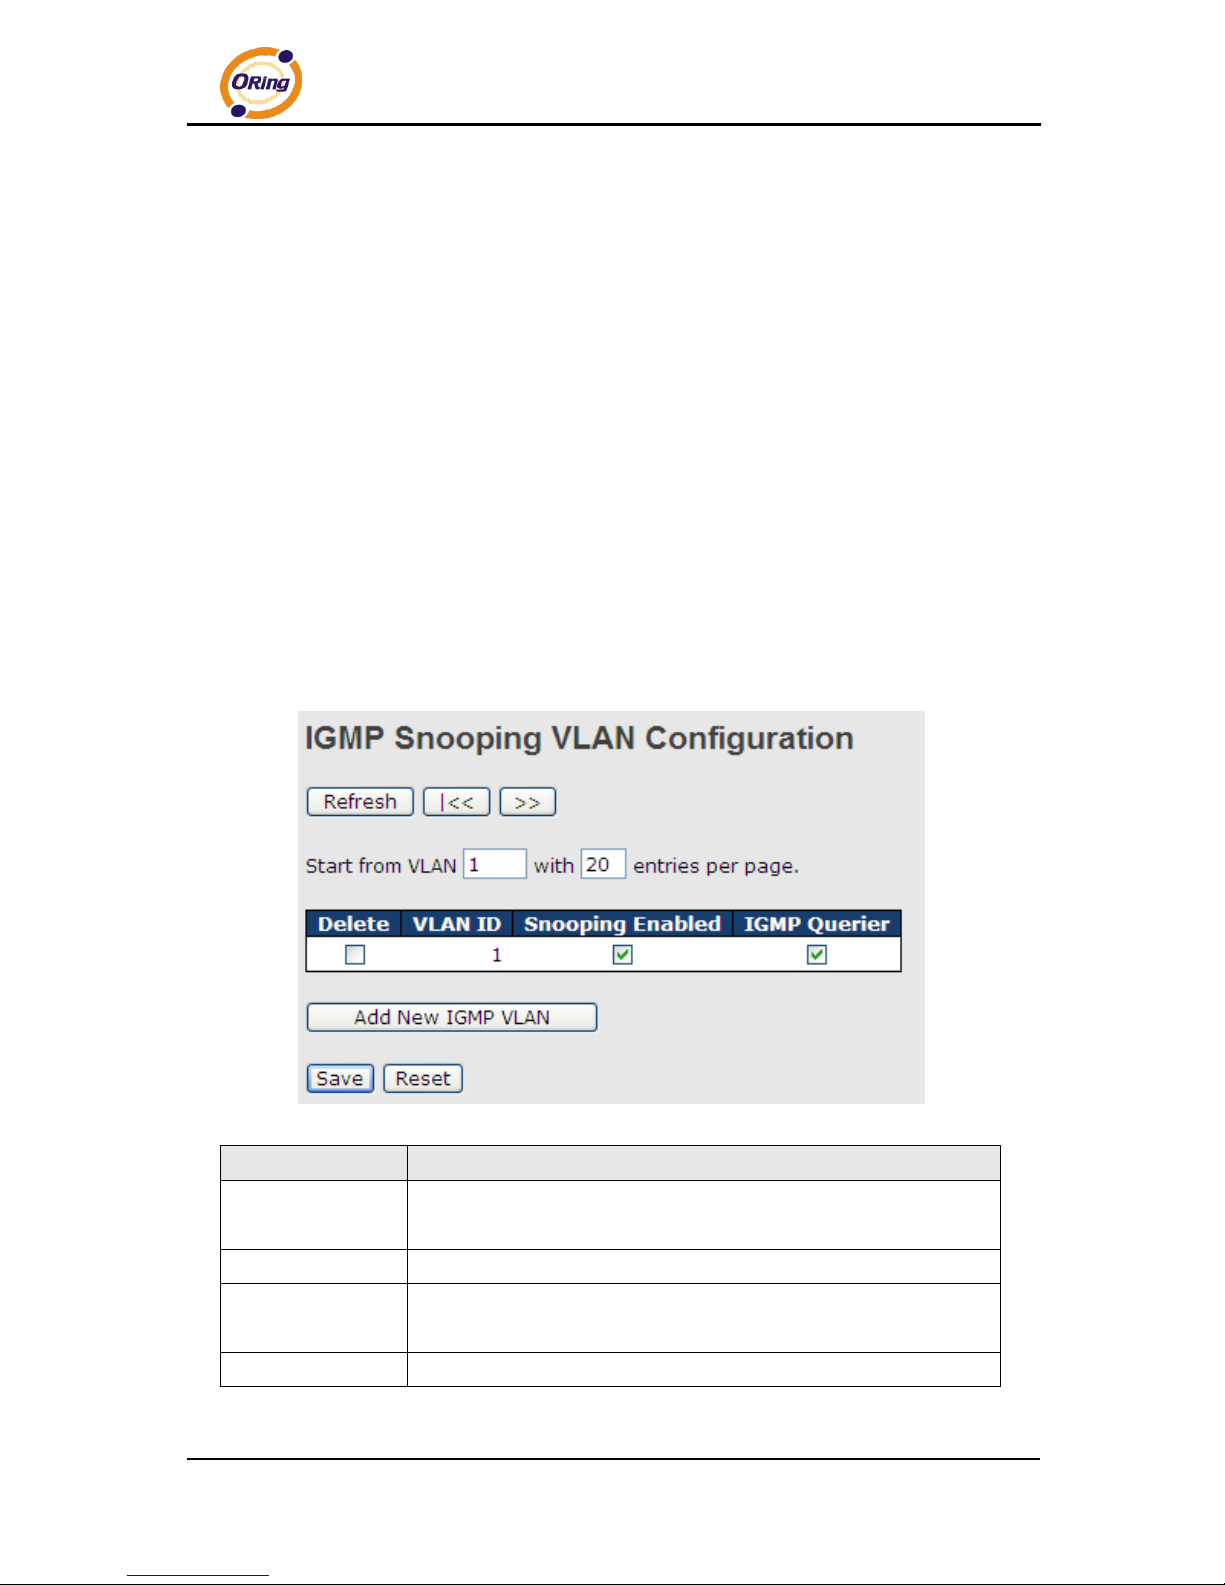
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
92
5.7.2 VLAN Configurations of IGMP Snooping
If a VLAN is not IGMP snooping-enabled, it floods multicast data and control packets to the
entire VLAN in hardware. When snooping is enabled, IGMP packets are trapped to the CPU.
Data packets are mirrored to the CPU in addition to being VLAN flooded. The CPU then
installs hardware resources, so that subsequent data packets can be switched to desired ports
in hardware without going to the CPU.
Each page shows up to 99 entries from the VLAN table, depending on the value in the Entries
Per Page field. By default, the page will show the first 20 entries from the beginning of the
VLAN table. The first displayed will be the one with the lowest VLAN ID found in the VLAN
Table.
The VLAN field allows the user to select the starting point in the VLAN Table. Clicking Refresh
will update the displayed table starting from that or the next closest VLAN Table match.
The >> button will use the last entry of the currently displayed entry as a basis for the next
lookup. When the end is reached, the text No more entries is shown in the displayed table.
Use the |<< button to start over.
Label
Description
Delete
Check to delete the entry. The designated entry will be deleted during
the next save.
VLAN ID
The VLAN ID of the entry
IGMP Snooping
Enable
Check to enable IGMP snooping for individual VLAN. Up to 32
VLANs can be selected.
IGMP Querier
Check to enable the IGMP Querier in the VLAN
Page 94
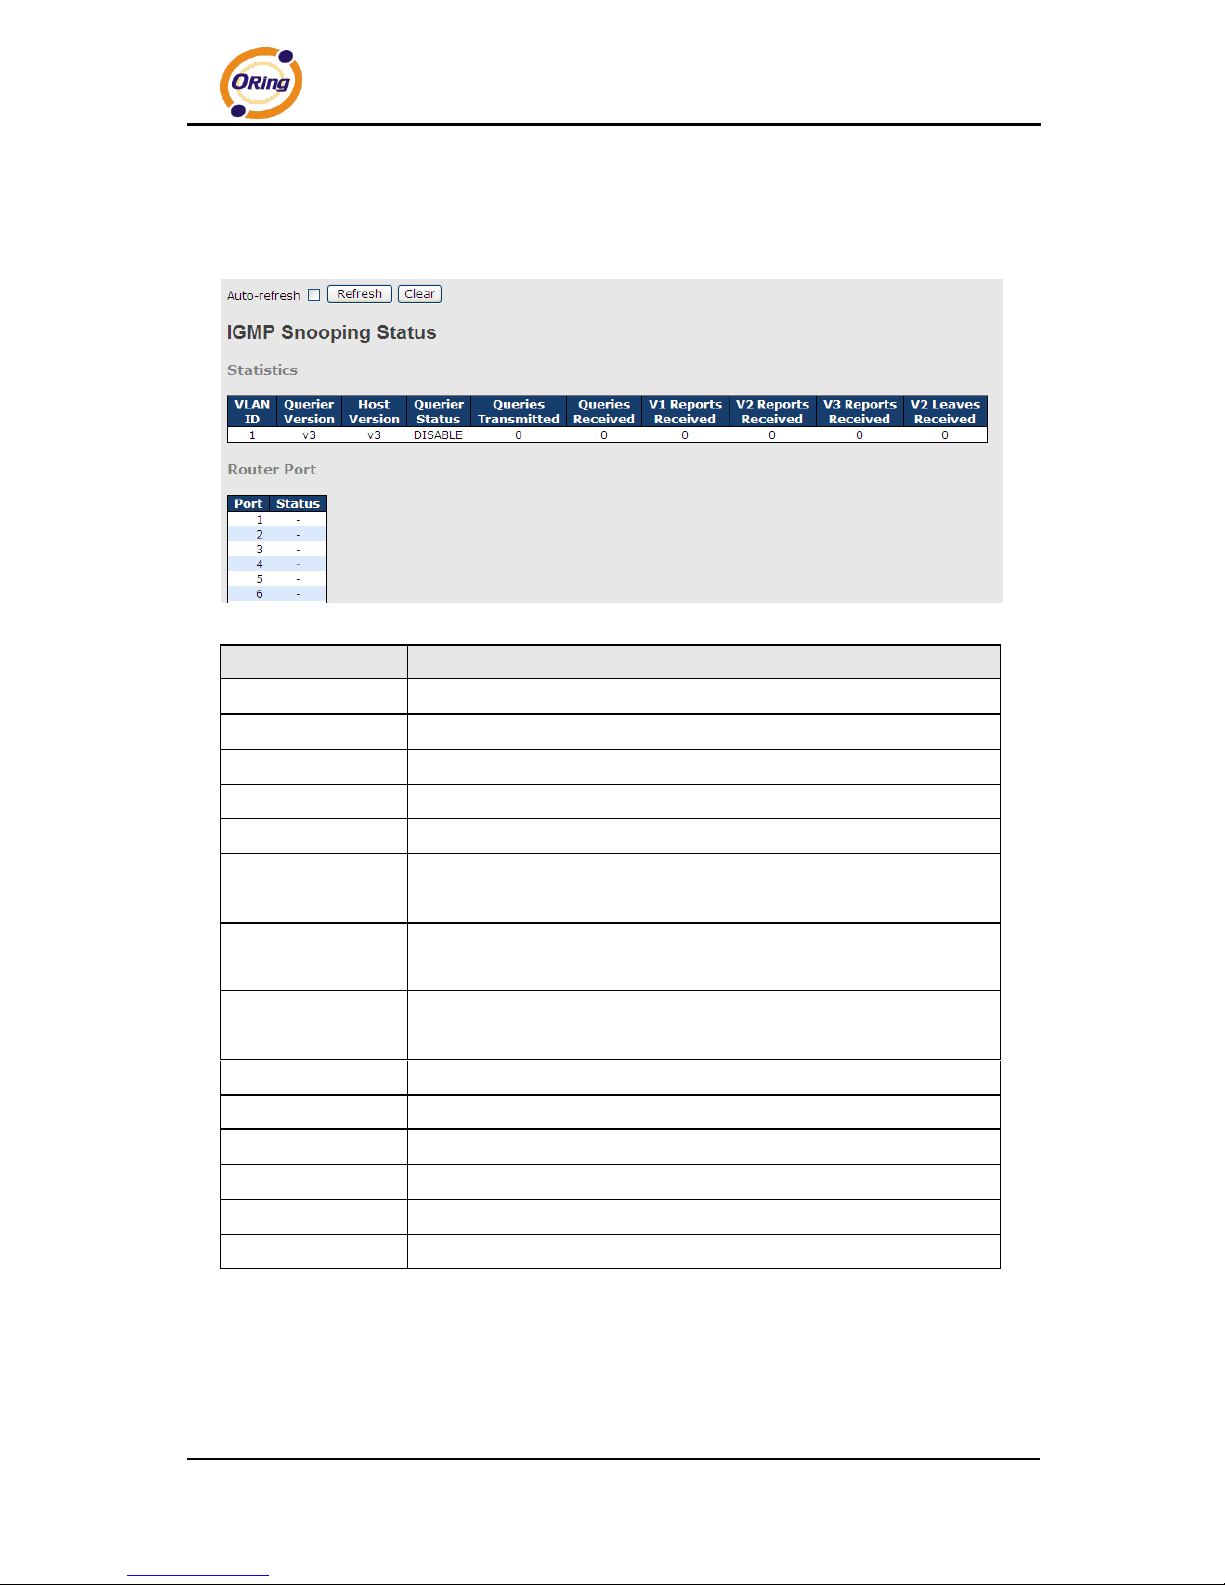
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
93
5.7.3 IGMP Snooping Status
This page provides IGMP snooping status.
Label
Description
VLAN ID
The VLAN ID of the entry
Querier Version
Active Querier version
Host Version
Active Host version
Querier Status
Shows the Querier status as ACTIVE or IDLE
Querier Receive
The number of transmitted Querier
V1 Reports
Receive
The number of received V1 reports
V2 Reports
Receive
The number of received V2 reports
V3 Reports
Receive
The number of received V3 reports
V2 Leave Receive
The number of received V2 leave packets
Refresh
Click to refresh the page immediately
Clear
Clear all statistics counters
Auto-refresh
Check to enable an automatic refresh of the page at regular intervals
Port
Switch port number
Status
Indicates whether a specific port is a router port or not
5.7.4 Groups Information of IGMP Snooping
Information about entries in the IGMP Group Table is shown in this page. The IGMP Group
Table is sorted first by VLAN ID, and then by group.
Page 95
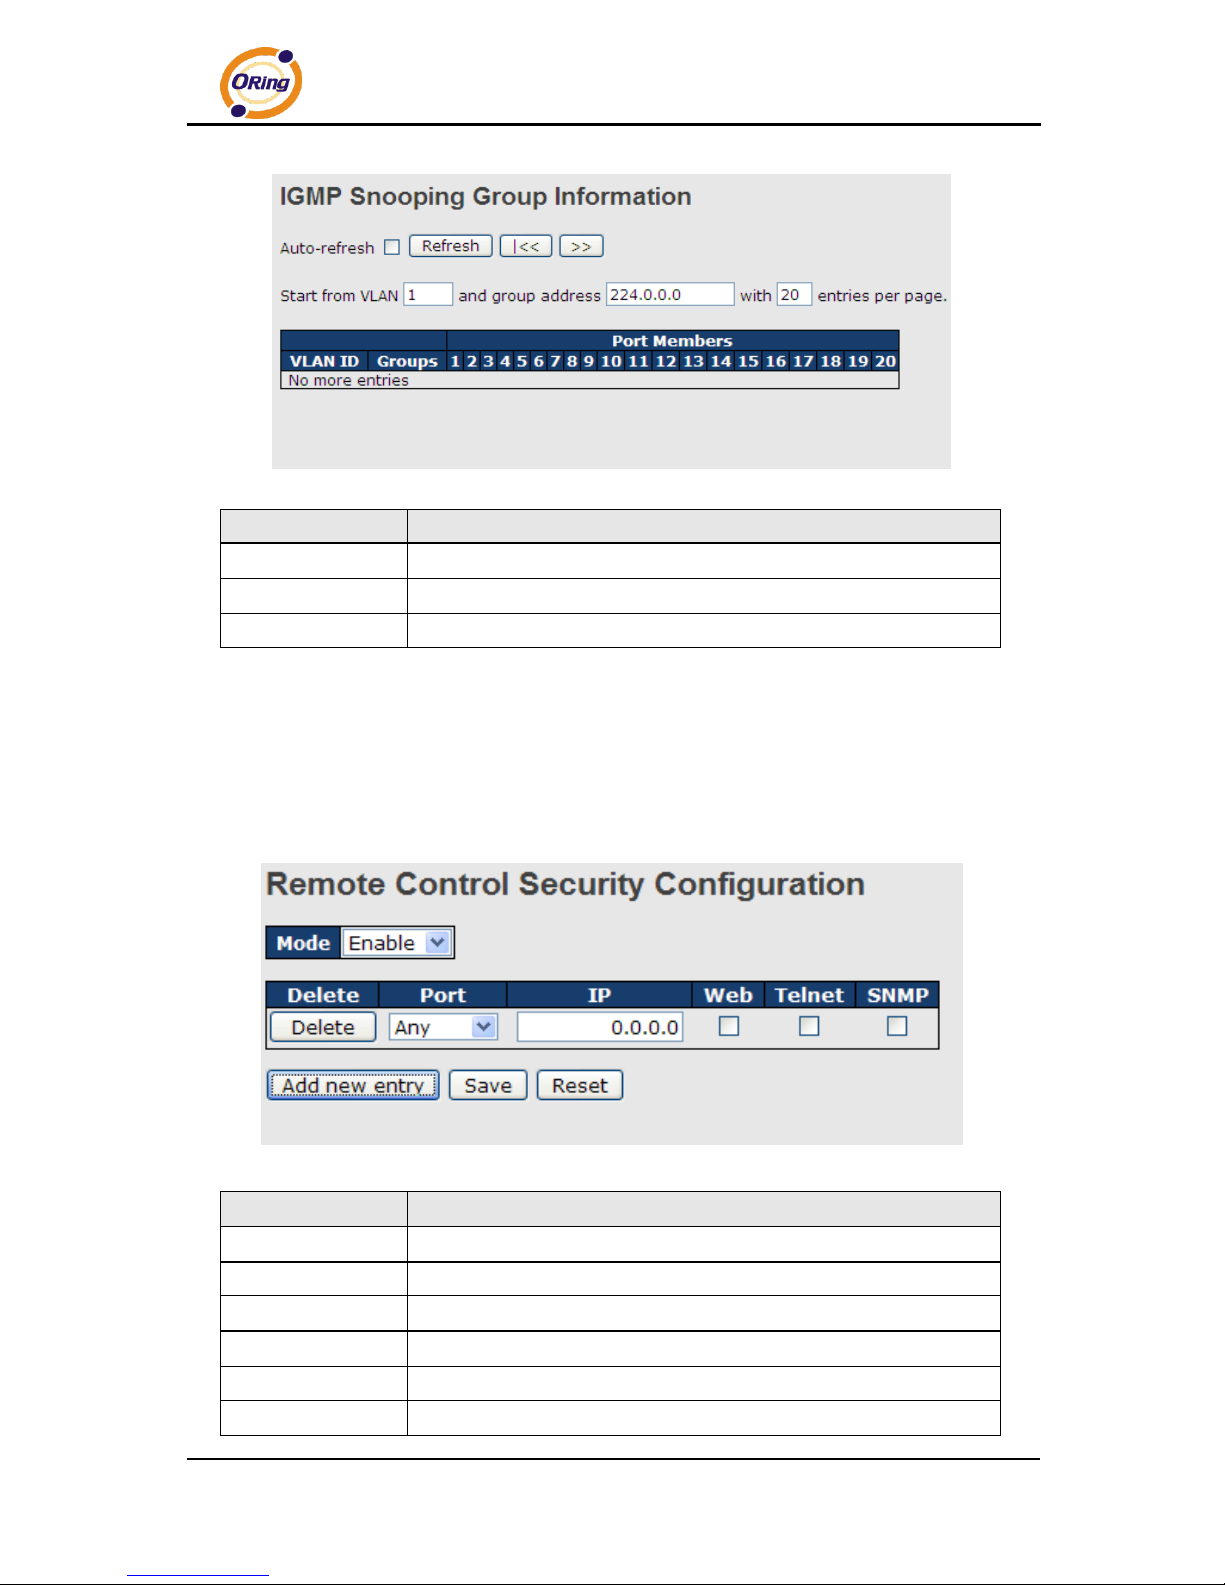
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
94
Label
Description
VLAN ID
The VLAN ID of the group
Groups
The group address of the group displayed
Port Members
Ports under this group
5.8 Security
5.8.1 Remote Control Security Configurations
Remote Control Security allows you to limit remote access to the management interface.
When enabled, requests of the client which is not in the allowed list will be rejected.
Label
Description
Port
Port number of the remote client
IP Address
IP address of the remote client. 0.0.0.0 means "any IP".
Web
Check to enable management via a Web interface
Telnet
Check to enable management via a Telnet interface
SNMP
Check to enable management via a SNMP interface
Delete
Check to delete entries
Page 96
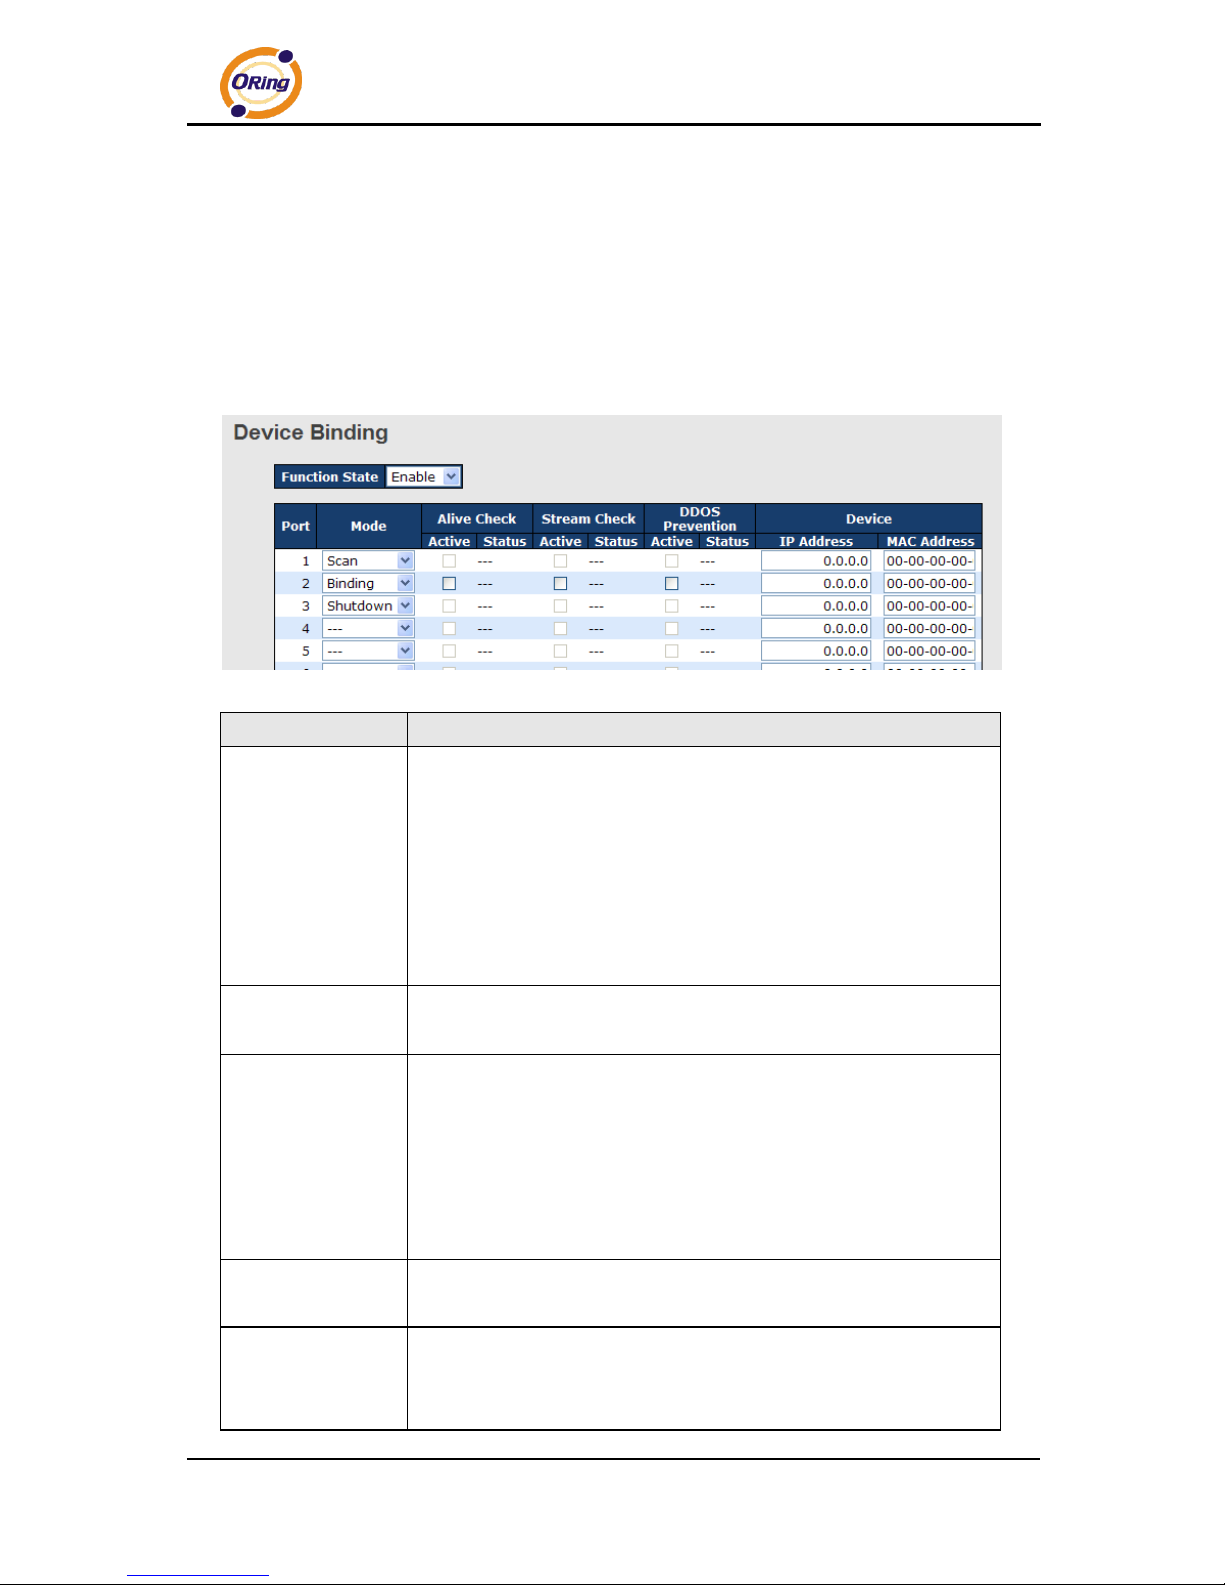
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
95
5.8.2 Device Binding
Device binding is ORing's proprietary technology which binds the IP/MAC address of a device
with a specified Ethernet port. If the IP/MAC address of the device connected to the Ethernet
port does not conform to the binding requirements, the device will be locked for security
concerns. Device Binding also provides security functions via alive checking, streaming check,
and DoS/DDoS prevention.
Label
Description
Mode
Indicates the device binding operation for each port. Possible modes
are:
---: disable
Scan: scans IP/MAC automatically, but no binding function
Binding: enables binding. Under this mode, any IP/MAC that does
not match the entry will not be allowed to access the network.
Shutdown: shuts down the port (No Link)
Alive Check
Active
Check to enable alive check. When enabled, switch will ping the
device continually.
Alive Check
Status
Indicates alive check status. Possible statuses are:
---: disable
Got Reply: receive ping reply from device, meaning the device is still
alive
Lost Reply: not receiving ping reply from device, meaning the device
might have been dead.
Stream Check
Active
Check to enable stream check. When enabled, the switch will detect
the stream change (getting low) from the device.
Stream Check
Status
Indicates stream check status. Possible statuses are:
---: disable
Normal: the stream is normal.
Page 97
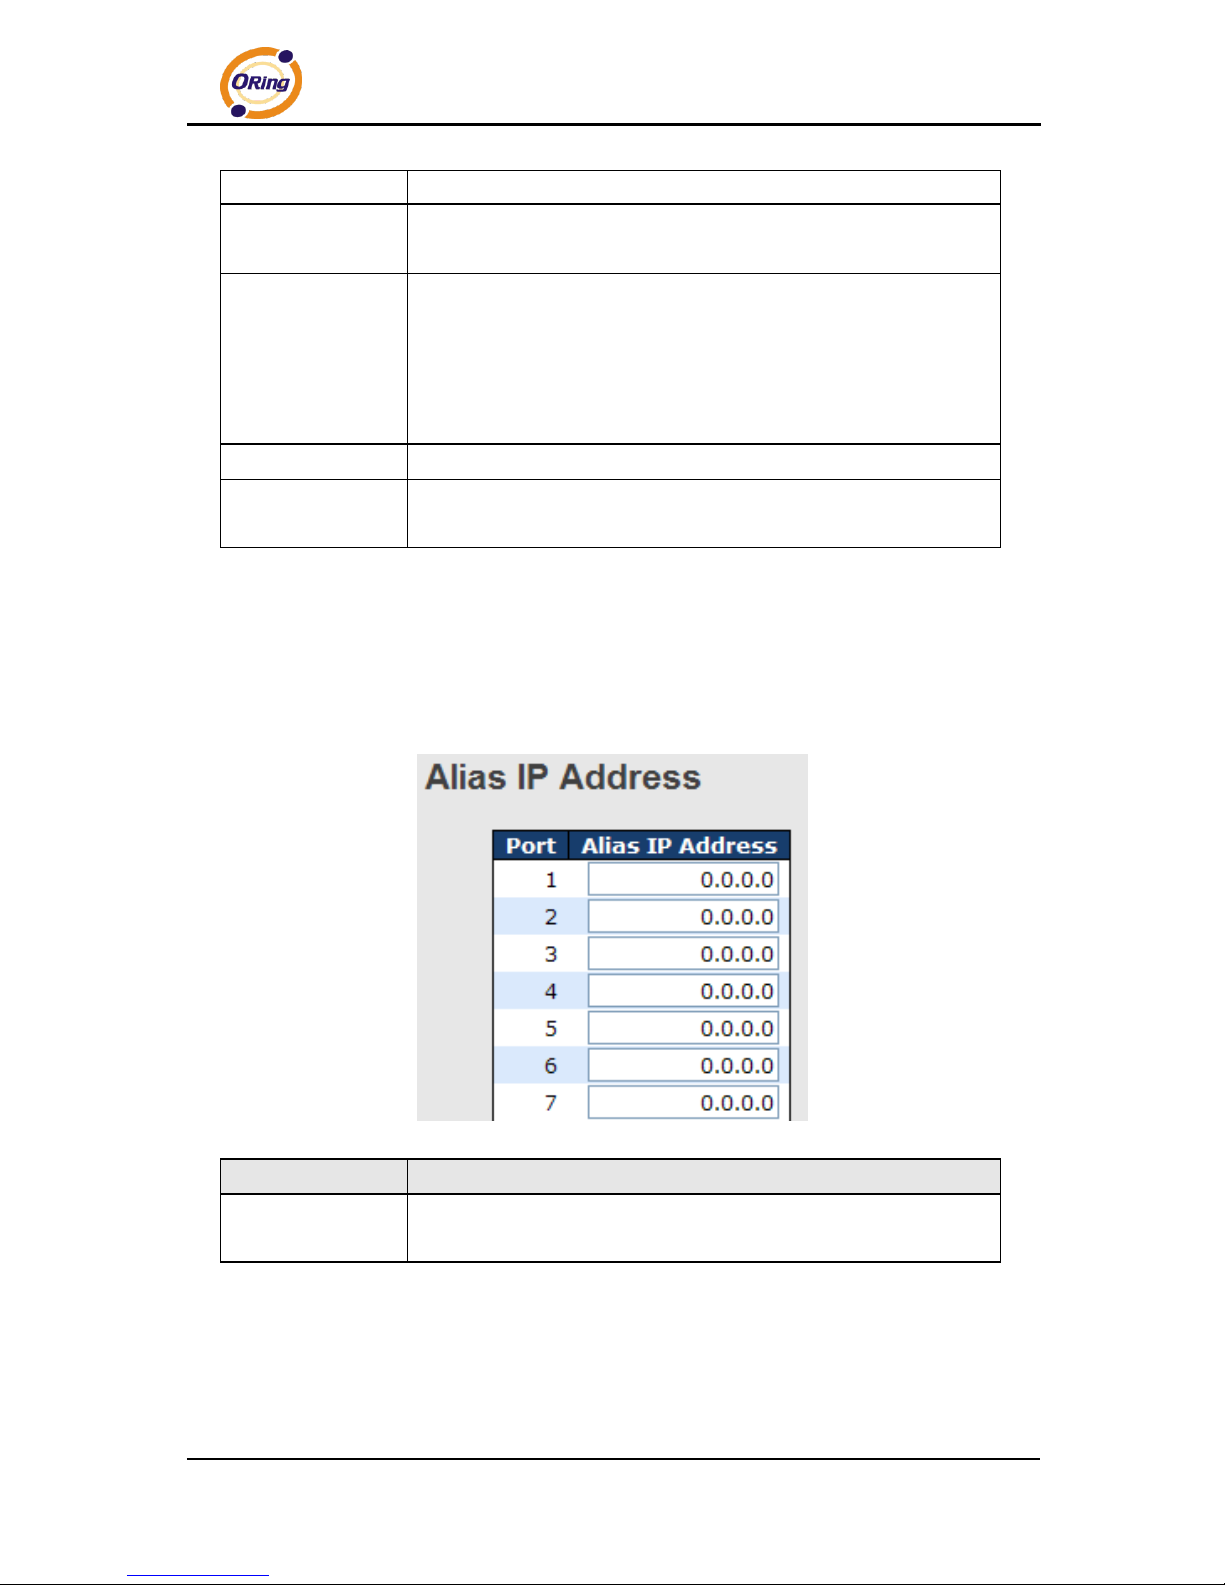
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
96
Low: the stream is getting low.
DDoS Prevention
Acton
Check to enable DDOS prevention. When enabled, the switch will
monitor the device against DDOS attacks.
DDoS Prevention
Status
Indicates DDOS prevention status. Possible statuses are:
---: disable
Analyzing: analyzes packet throughput for initialization
Running: analysis completes and ready for next move
Attacked: DDOS attacks occur
Device IP Address
Specifies IP address of the device
Device MAC
Address
Specifies MAC address of the device
Advanced Configurations
Alias IP Address
This page provides alias IP address configuration. Some devices might have more than one IP
addresses. You could specify other IP addresses here.
Label
Description
Alias IP Address
Specifies alias IP address. Keep 0.0.0.0 if the device does not have
an alias IP address.
Alive Check
Alive Checking monitors the real-time status of the device connected to the port.
Alive-checking packets will be sent to the device to probe if the device is running. If the switch
receives no response from the device, actions will be taken according to your configurations.
Page 98
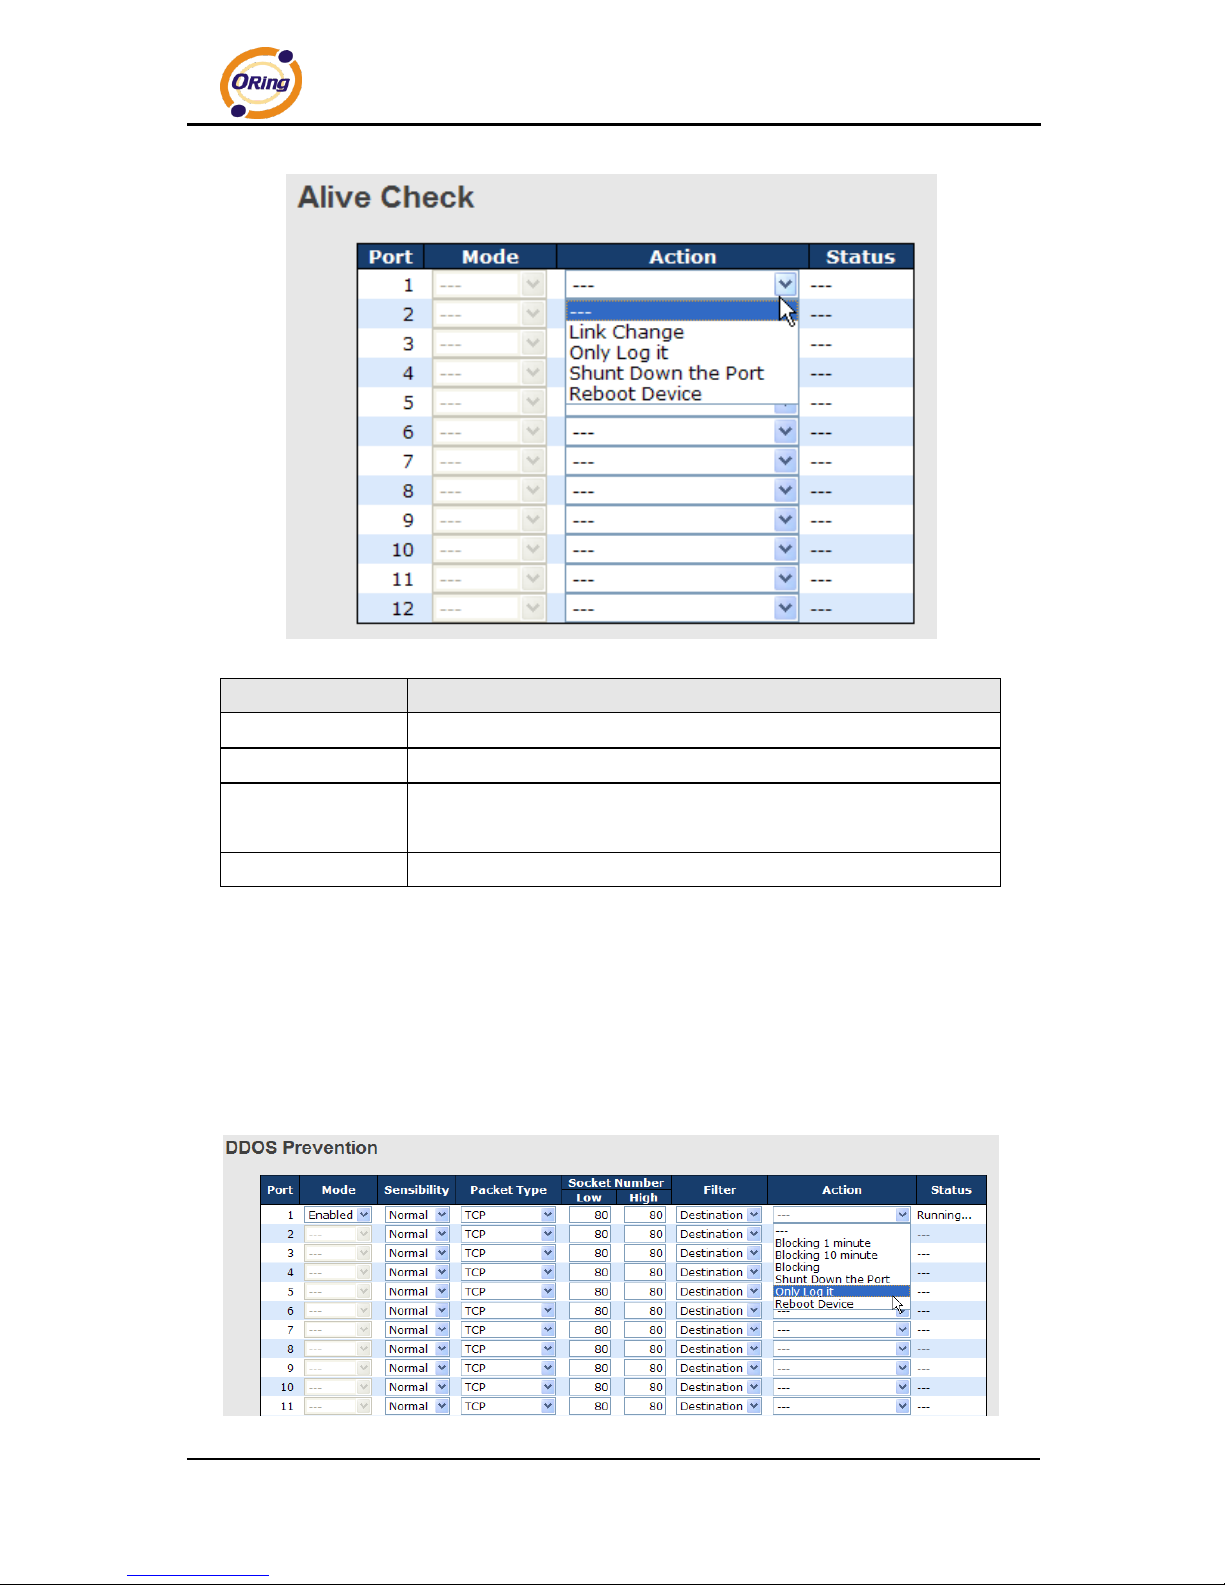
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
97
Label
Description
Link Change
Disables or enables the port
Only log it
Simply sends logs to the log server
Shunt Down the
Port
Disables the port
Reboot Device
Disables or enables PoE power
DDoS Prevention
The switch can monitor ingress packets, and perform actions when DDOS attack occurred on
this port. When network traffic from a specific device increases significantly in a short period of
time, the switch will lock the IP address of that device to protect the network from attacks. You
can configure DDoS prevention on this page to achieve maximum protection.
Page 99
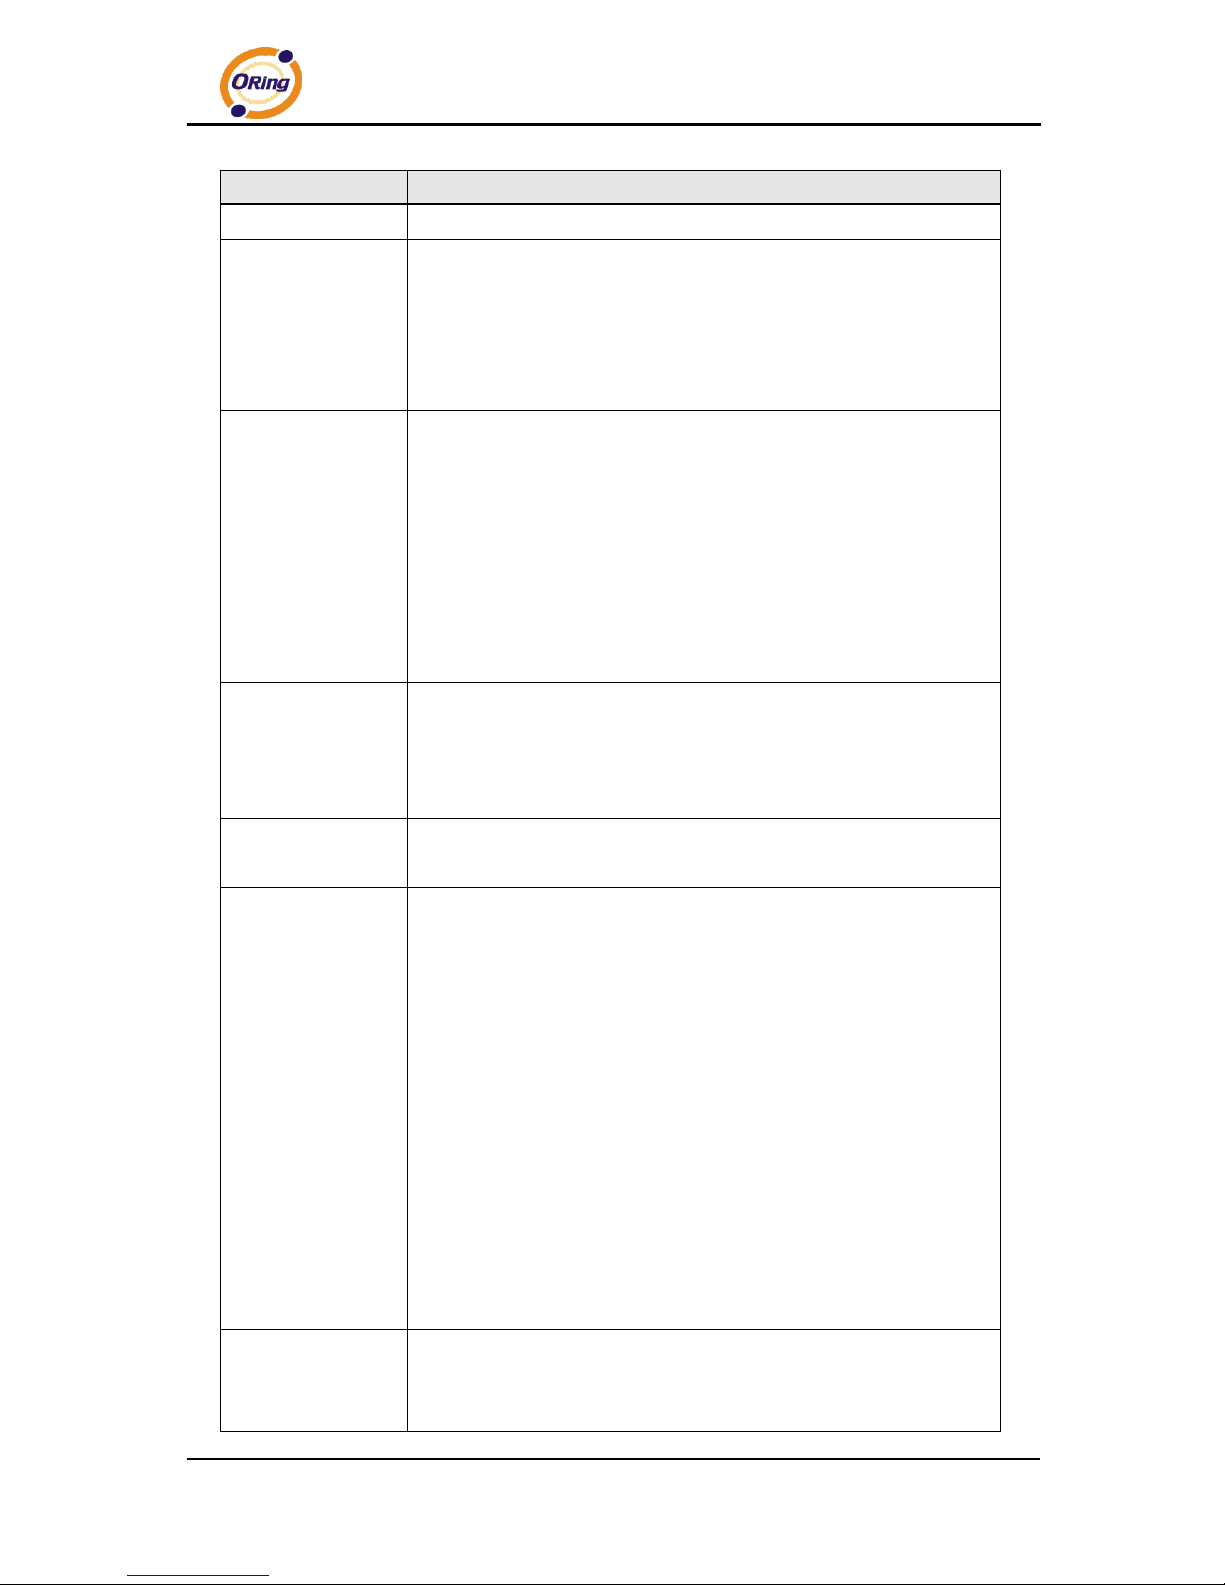
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
98
Label
Description
Mode
Enables or disables DDOS prevention of the port
Sensibility
Indicates the level of DDOS detection. Possible levels are:
Low: low sensibility
Normal: normal sensibility
Medium: medium sensibility
High: high sensibility
Packet Type
Indicates the types of DDoS attack packets to be monitored. Possible
types are:
RX Total: all ingress packets
RX Unicast: unicast ingress packets
RX Multicast: multicast ingress packets
RX Broadcast: broadcast ingress packets
TCP: TCP ingress packets
UDP: UDP ingress packets
Socket Number
If packet type is UDP (or TCP), please specify the socket number
here. The socket number can be a range, from low to high. If the
socket number is only one, please fill the same number in the low
and high fields.
Filter
If packet type is UDP (or TCP), please choose the socket direction
(Destination/Source).
Action
Indicates the action to take when DDOS attacks occur. Possible
actions are:
---: no action
Blocking 1 minute: blocks the forwarding for 1 minute and log the
event
Blocking 10 minute: blocks the forwarding for 10 minutes and log
the event
Blocking: blocks and logs the event
Shunt Down the Port: shuts down the port (No Link) and logs the
event
Only Log it: simply logs the event
Reboot Device: if PoE is supported, the device can be rebooted.
The event will be logged.
Status
Indicates the DDOS prevention status. Possible statuses are:
---: disables DDOS prevention
Analyzing: analyzes packet throughput for initialization
Page 100
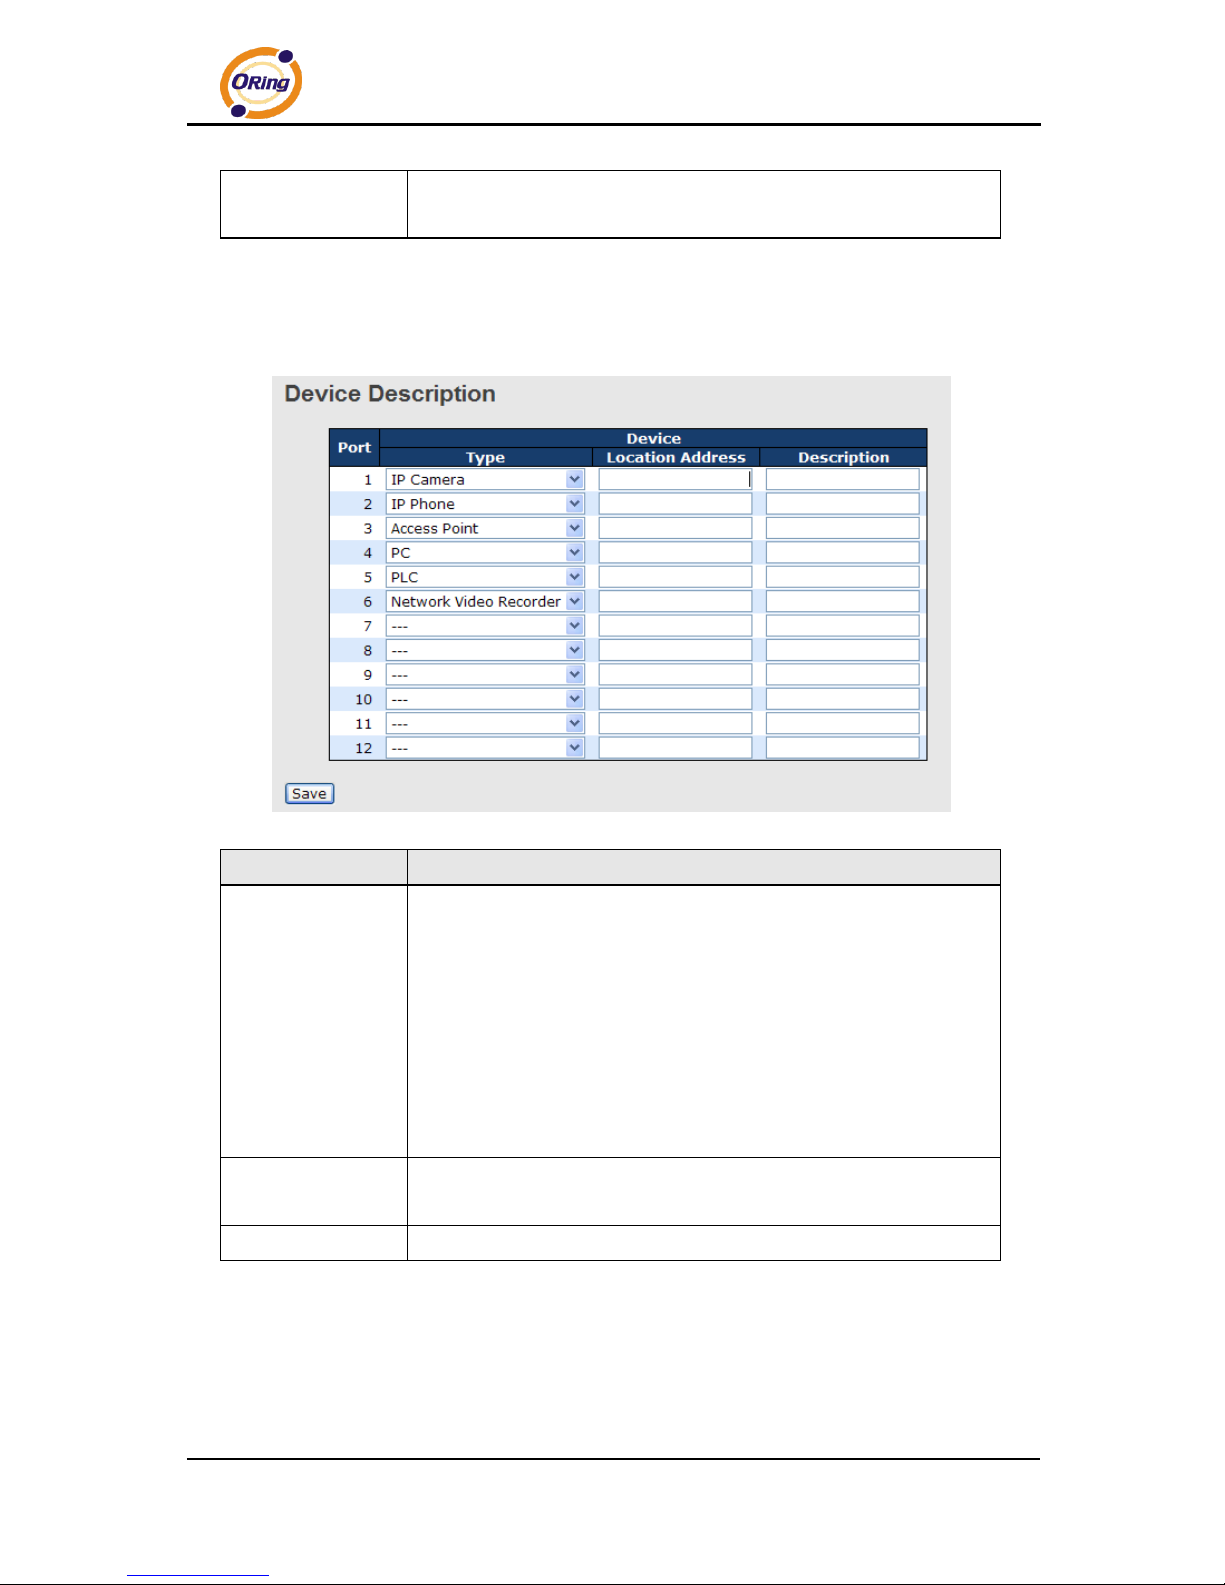
IGS-9844/9848GPF Series User Manual
ORing Industrial Networking Corp
99
Running: analysis completes and ready for next move
Attacked: DDOS attacks occur
Device Description
This page allows you to configure device description settings.
Label
Description
Device Type
Indicates device types. Possible types are:
---: no specification
IP Camera
IP Phone
Access Point
PC
PLC
Network Video Recorder
Location Address
Indicates location information of the device. The information can be
used for Google Mapping.
Description
Device descriptions
Stream Check
Stream check monitors the consistency of real-time network traffic from the device bound with
the port. When the traffic changes sharply all of a sudden, an alert will be issued. This page
allows you to configure stream check settings.
 Loading...