

Page 1
LevelOne
User Manual
WBR-6600
N_Max Wireless ADSL2+ Modem Router
V1.0 – 0811
Page 2
2
Table of Contents
TABLE OF CONTENTS ..................................................................................................................................... 2
CHAPTER 1 - INTRODUCTION ........................................................................................................................ 6
Introducing the WBR-6600 ........................................................................................................................ 6
Features .................................................................................................................................................... 8
Installation Diagram of the WBR-6600 ................................................................................................... 12
CHAPTER 2 - PRODUCT OVERVIEW ........................................................................................................... 13
Standards-Based Technology ................................................................................................................. 13
Installation Considerations ...................................................................................................................... 13
Package Contents ................................................................................................................................... 14
Important Notes....................................................................................................................................... 14
The Front LEDs - WBR-6600 .................................................................................................................. 15
The Rear Ports - WBR-6600 ................................................................................................................... 16
Antenna Position Placement ................................................................................................................... 18
Cabling .................................................................................................................................................... 18
CHAPTER 3 - INSTALLATION ........................................................................................................................ 19
Before Configuration ............................................................................................................................... 19
Factory Default Settings .......................................................................................................................... 24
LAN and WAN Port Addresses ............................................................................................................... 25
Information from your ISP ....................................................................................................................... 25
Configuring with your WBR-6600............................................................................................................ 26
CHAPTER 4 – BASIC CONFIGURATION ....................................................................................................... 30
Status Page ............................................................................................................................................. 31
Quick Start ............................................................................................................................................... 32
Set Wireless Configuration ............................................................................................................. 33
WAN ........................................................................................................................................................ 34
WLAN ...................................................................................................................................................... 35
Wireless Security Parameters................................................................................................................. 36
WPA Pre-Shared Key ..................................................................................................................... 36
WPA2 Pre-Shared Key ................................................................................................................... 36
WPA/WPA2 Pre-Shared Key .......................................................................................................... 37
WEP ............................................................................................................................................... 38
Page 3
3
CHAPTER 5 – ADVANCE CONFIGURATION ................................................................................................ 39
Status Page ............................................................................................................................................. 40
ADSL Status ................................................................................................................................... 42
Operational Mode ........................................................................................................................... 43
ARP Table....................................................................................................................................... 44
DHCP Table .................................................................................................................................... 45
System Log .................................................................................................................................... 46
Firewall Log .................................................................................................................................... 47
UPnP Portmap ............................................................................................................................... 48
Quick Start ............................................................................................................................................... 49
ADSL .............................................................................................................................................. 49
EWAN ............................................................................................................................................. 50
Set Wireless Configuration ............................................................................................................. 56
Configuration ........................................................................................................................................... 57
LAN (Local Area Network) ...................................................................................................................... 58
Ethernet .......................................................................................................................................... 59
IP Alias............................................................................................................................................ 59
Wireless .......................................................................................................................................... 60
Wireless Distribution System (WDS).............................................................................................. 62
Wireless Security............................................................................................................................ 62
WPA Pre-Shared Key ..................................................................................................................... 63
WPA2 Pre-Shared Key ................................................................................................................... 64
WPA/WPA2 Pre-Shared Key .......................................................................................................... 65
WEP ............................................................................................................................................... 66
Wi-Fi Protected Setup (WPS) ........................................................................................................ 67
DHCP Server .................................................................................................................................. 77
WAN (Wide Area Network)...................................................................................................................... 79
WAN Profile .................................................................................................................................... 80
ADSL Mode .................................................................................................................................... 86
System .................................................................................................................................................... 88
Time Zone ............................................................................................................................................... 89
Firmware Upgrade .................................................................................................................................. 90
Backup / Restore .................................................................................................................................... 91
Page 4
4
Restart Router ......................................................................................................................................... 92
User Management .................................................................................................................................. 93
Mail Alert ................................................................................................................................................. 94
Firewall .................................................................................................................................................... 95
Packet Filter ................................................................................................................................... 97
MAC Filter ...................................................................................................................................... 99
Block WAN PING ......................................................................................................................... 102
URL Filter ..................................................................................................................................... 103
QoS (Quality of Service) ....................................................................................................................... 106
Virtual Server ......................................................................................................................................... 112
Port Mapping ................................................................................................................................. 114
DMZ ............................................................................................................................................... 116
Wake on LAN ......................................................................................................................................... 117
Time Schedule ....................................................................................................................................... 118
Time Schedule ....................................................................................................................................... 118
Advanced ............................................................................................................................................... 119
Static Route .................................................................................................................................. 120
Static ARP .................................................................................................................................... 120
Dynamic DNS ............................................................................................................................... 121
VLAN ............................................................................................................................................ 122
Device Management .................................................................................................................... 123
IGMP ............................................................................................................................................ 131
SNMP Access Control .................................................................................................................. 131
Remote Access ............................................................................................................................ 134
Save Configuration to Flash .................................................................................................................. 135
Restart ................................................................................................................................................... 135
Logout ................................................................................................................................................... 136
CHAPTER 6 - TROUBLESHOOTING ........................................................................................................... 137
REGULATORY APPROVALS ........................................................................................................................ 139
FCC Statement...................................................................................................................................... 139
CE Approval .......................................................................................................................................... 140
General Public License ......................................................................................................................... 140
Page 5
5
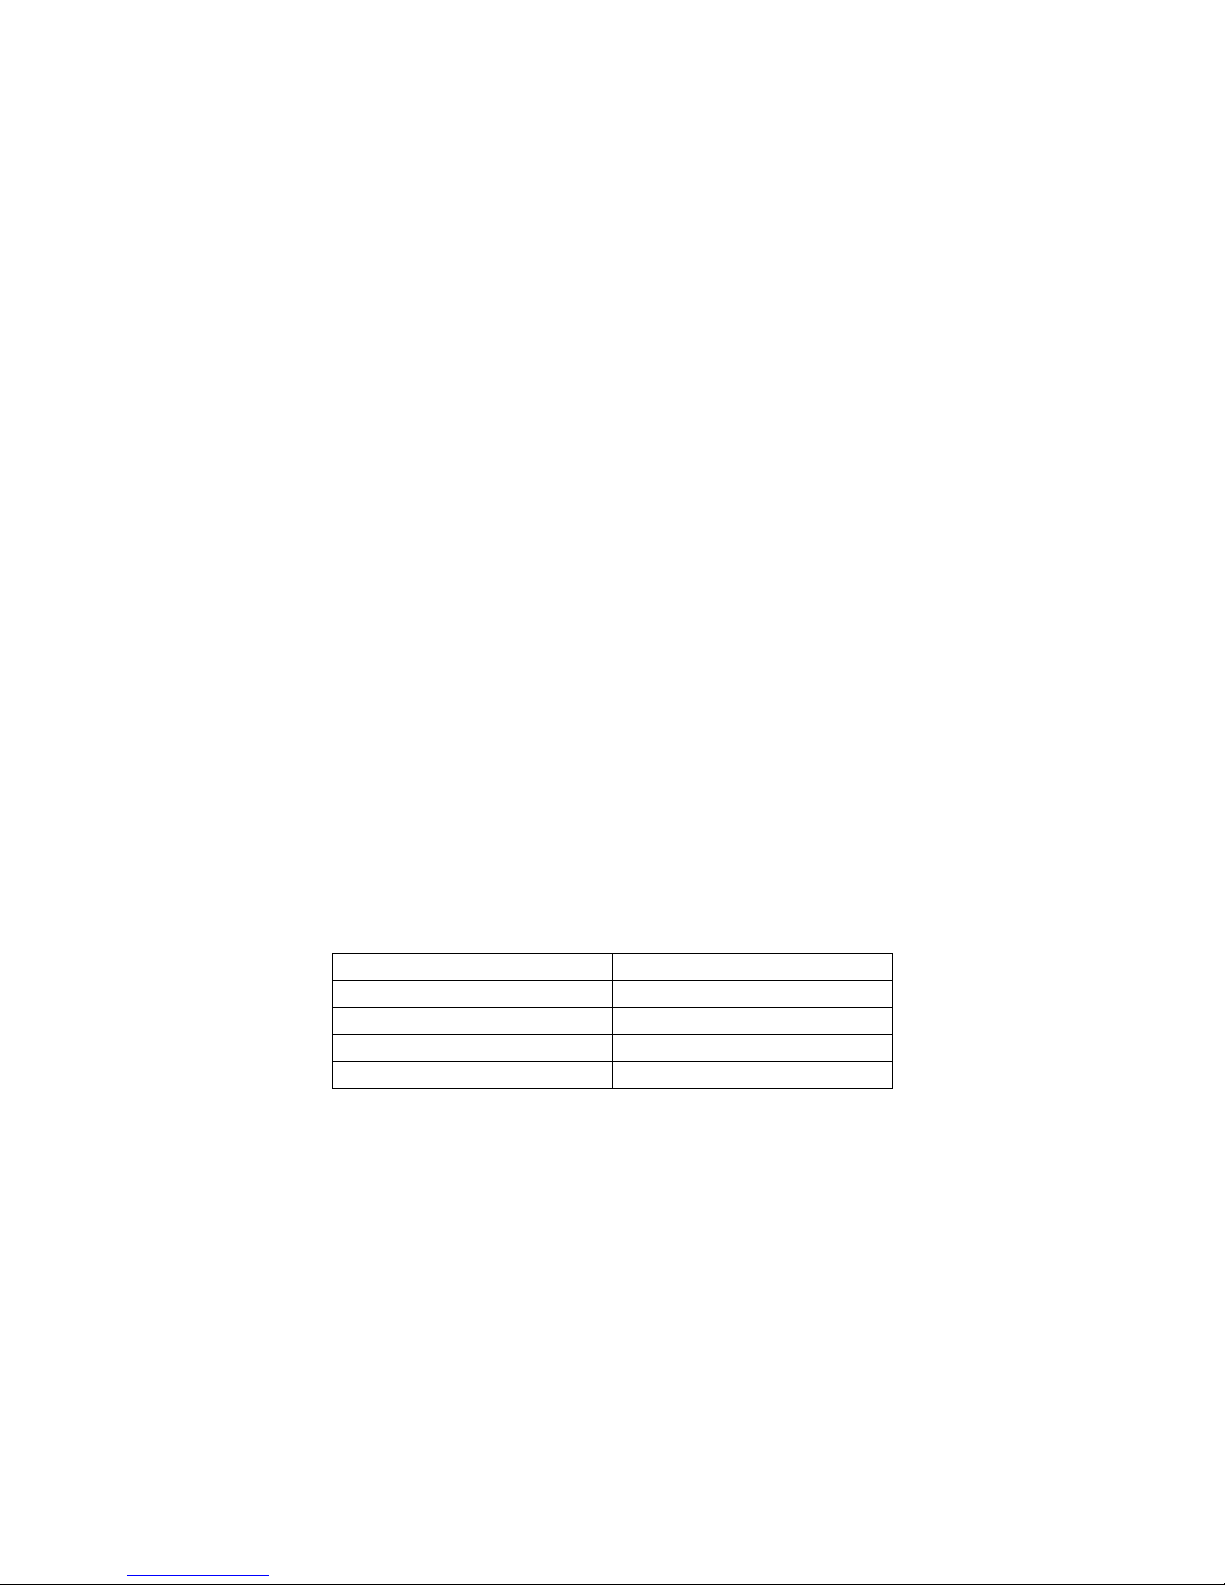
Default Settings
IP Address
192.168.0.1
Admin / Password
admin / password
Wireless Mode
Enable
SSID
WBR-6600
Security
None
Page 6
6
Chapter 1 - Introduction
Introducing the WBR-6600
Thank you for purchasing the WBR-6600 Router. Your new router is an all-in-one unit that
combines an ADSL modem, ADSL2/2+ router and Ethernet network switch to provide
everything you need to get the machines on your network connected to the Internet over an
ADSL broadband connection.
The WBR-6600 router complies with ADSL2+ standards for deployment worldwide and
supports downstream rates of up to 24 Mbps and upstream rates of up to 1 Mbps. Designed
for small office, home office and residential users, the router enables even faster Internet
connections. You can enjoy ADSL services and broadband multimedia applications such as
interactive gaming, video streaming and real-time audio much easier and faster than ever
before.
The WBR-6600 supports PPPoA (RFC 2364 – PPP (Point-to-Point Protocol) over ATM
Adaptation Layer 5), RFC 1483 encapsulation over ATM (bridged or routed), PPP over
Ethernet (RFC 2516) to establish a connection with your ISP. Your new router also supports
VC-based and LLC-based multiplexing.
The perfect solution for connecting a small group of PCs to a high-speed broadband Internet
connection, the WBR-6600 allows multiple users to have high-speed Internet access
simultaneously.
Your new router also serves as an Internet firewall, protecting your network from access by
outside users. Not only does it provide a natural firewall function with Network Address
Translation (NAT), it also provides rich firewall features to secure your network. All incoming
data packets are monitored and filtered. You can also configure your new router to block
internal users from accessing the Internet.
The WBR-6600 provides two levels of security support. First, it masks LAN IP addresses
making them invisible to outside users on the Internet, so it is much more difficult for a
hacker to target a machine on your network. Second, it can block and redirect certain ports
to limit the services that outside users can access. To ensure that games and other Internet
applications run properly, you can open specific ports for outside users to access internal
services on your network.
Page 7
7
The Integrated DHCP (Dynamic Host Control Protocol) client and server services allow
multiple users to get IP addresses automatically when the router boots up. Simply set local
machines as a DHCP client to accept a dynamically assigned IP address from the DHCP
server and reboot. Each time a local machine is powered up; the router recognizes it and
assigns an IP address to instantly connect it to the LAN.
For advanced users, Virtual Service (port mapping) functions allow the product to provide
limited visibility to local machines with specific services for outside users. For instance, a
dedicated web server can be connected to the Internet via the router and then incoming
requests for web pages that are received by the router can be rerouted to your dedicated
local web server, even though the server now has a different IP address.
Virtual Server can also be used to re-task services to multiple servers. For instance, you can
set the router to allow separated FTP, Web, and Multiplayer game servers to share the same
Internet-visible IP address while still protecting the servers and LAN users from hackers.
Page 8
8
Features
Express Internet Access – ADSL2/2+ capable
The WBR-6600 complies with ADSL worldwide standards. Supporting downstream rates of
8Mbps with ADSL, the router is capable of up to 12/24 Mbps with ADSL2/2+, and upstream
rates of up to 1 Mbps. Users enjoy not only high-speed ADSL services but also broadband
multimedia applications such as interactive gaming, video streaming and real-time audio
which are easier and faster than ever. The router is compliant with Multi-Mode standard
(ANSI T1.413, Issue 2; G.dmt (ITU G.992.1); G.hs (ITU G994.1); G.dmt.bis (ITU G.992.3);
and G.dmt.bisplus (ITU G.992.5)
802.11n Wireless AP with WPA Support
With integrated 802.11n Wireless Access Point in the router, the device offers a quick and
easy access among wired network, wireless network and broadband connection (ADSL)
with single device simplicity, and as a result, mobility to the users. In addition to 300 Mbps
802.11n data rate, it also interoperates backward with existing 802.11g and 802.11b
equipment. The Wireless Protected Access (WPA) and Wireless Encryption Protocol (WEP)
supported features enhance the security level of data protection and access control via
Wireless LAN.
Fast Ethernet Switch
A 4-port 10/100Mbps fast Ethernet switch is built-in with automatic switching between MDI
and MDI-X for 10Base-T and 100Base-TX ports, with auto detection allowing you to use
either straight or cross-over Ethernet cables.
EWAN
Besides using ADSL to get connected to the Internet, WBR-6600 offers its Ethernet port 1
as a WAN port to be used to connect to Cable Modems, VDSL, fiber optic lines and PON.
This alternative, yet faster method to connect to the internet will provide users more flexibility
to get online.
Page 9
9
Multi-Protocol to Establish a Connection
The router supports PPPoA (RFC 2364 - PPP over ATM Adaptation Layer 5), RFC 1483
encapsulation over ATM (bridged or routed), PPP over Ethernet (RFC 2516) to establish a
connection with an ISP. The router also supports VC-based and LLC-based multiplexing.
Universal Plug and Play (UPnP) and UPnP NAT Traversal
This protocol is used to enable simple and robust connectivity among stand-alone devices
and PCs from many different vendors, and it makes setting up a network simple and
affordable. UPnP architecture leverages TCP/IP and the Web to enable proximity
networking in addition to control and data transfer among networked devices. With this
feature enabled, you can seamlessly connect to Net Meeting or MSN Messenger.
Network Address Translation
Network Address Translation (NAT) allows multiple users to access outside resources such
as the Internet simultaneously with one IP address/one Internet access account. Many
application layer gateways (ALG) are supported such as web browser, ICQ, FTP, Telnet,
E-mail, News, Net2phone, Ping, NetMeeting, IP phone and others.
Firewall
NAT technology supports simple firewalls and provides options for blocking access from the
Internet, like Telnet, FTP, TFTP, WEB, SNMP and IGMP.
Domain Name Server Relay
Domain Name Server (DNS) relay provides an easy way to map a domain name with a
user-friendly name such as www.google.com with an IP address. When a local machine
sets its DNS server to the router‟s IP address, every DNS conversion request packet from
the PC to this router is forwarded to the real DNS on the outside network.
Dynamic Domain Name Server (DDNS)
The Dynamic DNS service allows you to alias a dynamic IP address to a static hostname.
This dynamic IP address is the WAN IP address. To use the service, you must first apply for
an account from a DDNS service such as http://www.dyndns.org/.
Page 10
10
PPP over Ethernet (PPPoE)
The WBR-6600 provides an embedded PPPoE client function to establish a connection.
You get greater access speed without changing the operation concept, while sharing the
same ISP account and paying for one access account. No PPPoE client software is required
for the local computer. Automatic Reconnect and Disconnect Timeout (Idle Timer) functions
are also provided.
Quality of Service (QoS)
QoS gives you full control over which types of outgoing data traffic should be given priority
by the router, ensuring important data like gaming packets, customer information, or
management information move through the router at lightning speed, even under heavy load.
The QoS features are configurable by Internal IP address, External IP address, protocol,
and port. You can throttle the speed at which different types of outgoing data pass through
the router, to ensure P2P users don‟t saturate upload bandwidth, or office browsing doesn‟t
bring client web serving to a halt. In addition, or alternatively, you can simply change the
priority of different types of upload data and let the router sort out the actual speeds.
Virtual Server:
You can specify which services are visible to outside users. The router detects an incoming
service request and forwards it to the specific local computer for handling. For example, you
can assign a PC in a LAN to act as a Web server inside and expose it to the outside network.
Outside users can browse inside the web server directly while it is protected by NAT. A DMZ
host setting is also provided for local computers exposed to the outside Internet network.
Dynamic Host Configuration Protocol (DHCP) Client and Server
On a WAN site, the DHCP client obtains an IP address from the Internet Service Provider
(ISP) automatically. On a LAN site, the DHCP server allocates a range of client IP
addresses, including subnet masks and DNS IP addresses and distributes them to local
computers. This provides an easy way to manage the local IP network.
Rich Packet Filtering
This feature filters the packet based on IP addresses as well as Port numbers. Filtering
packets to and from the Internet provides a higher level of security control.
Page 11
11
Web-based GUI
A web-based GUI offers easy configuration and management. It also supports remote
management capability for remote users to configure and manage this product.
Firmware Upgradeable
You can upgrade the router with the latest firmware through its web-based GUI.
Page 12
12
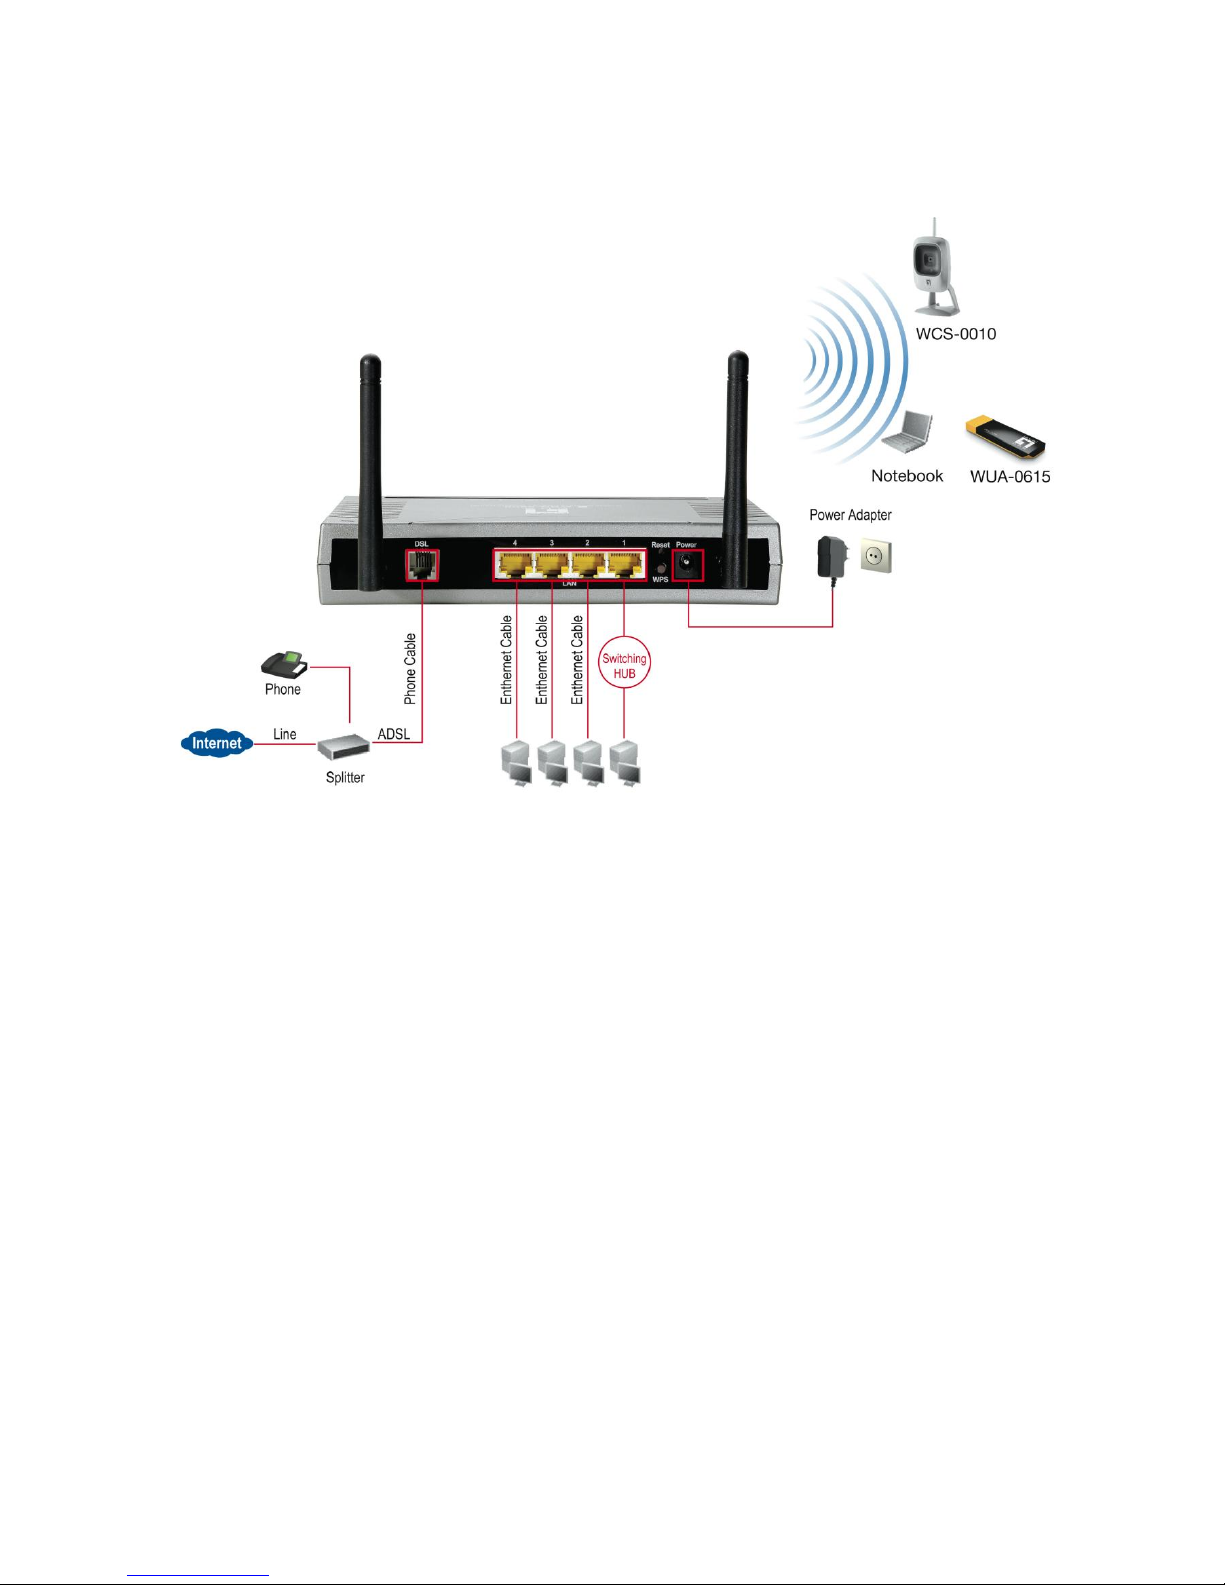
Installation Diagram of the WBR-6600
Page 13
13
Chapter 2 - Product Overview
Standards-Based Technology
The WBR-6600 Wireless Router utilizes the 802.11n standard. The IEEE 802.11n standard
is an extension of the 802.11g standard. It increases the data rate up to 300 Mbps within the
2.4GHz band, utilizing OFDM technology. This means that in most environments, within the
specified range of this device, you will be able to transfer large files quickly or even watch a
movie in MPEG format over your network without noticeable delays. This technology works
by transmitting high-speed digital data over a radio wave utilizing OFDM (Orthogonal
Frequency Division Multiplexing) technology. OFDM works by splitting the radio signal into
multiple smaller sub-signals that are then transmitted simultaneously at different frequencies
to the receiver. OFDM reduces the amount of crosstalk (interference) in signal
transmissions.
Installation Considerations
The WBR-6600 Wireless Router lets you access your network, using a wireless connection,
from virtually anywhere within its operating range. Keep in mind, however, that the number,
thickness and location of walls, ceilings, or other objects that the wireless signals must pass.
Keep the number of walls and ceilings between the WBR-6600 and other network devices to
a minimum - each wall or ceiling can reduce your WBR-6600 wireless product‟s range from
3-90 feet (1-30 meters.)
Position your devices so that the number of walls or ceilings is minimized. Be aware of the
direct line between network devices. Position the devices so that the signal will travel
straight through a wall or ceiling (instead of at an angle) for better reception. Building
Materials can impede the wireless signal - a solid metal door or aluminium studs may have a
negative effect on range.
Try to position wireless devices and computers with wireless adapters so that the signal
passes through drywall or open doorways and not other materials. Keep your product away
(at least 3-6 feet or 1-2 meters) from electrical devices or appliances that generate extreme
RF (radio frequency) noise.
Page 14
14
Package Contents
WBR-6600 N_Max Wireless ADSL2+ Modem Router
CD-ROM containing the online manual
2x Antennas
RJ-11 ADSL/Telephone Cable
Ethernet (CAT-5 LAN) Cable
AC-DC power adapter (12V DC, 1A)
Quick Installation Guide
Important Notes
Warning:
Do not use the WBR-6600 in high humidity or high temperatures.
Do not use the same power source for the WBR-6600 as other equipment.
Do not open or repair the case yourself. If the WBR-6600 is too hot, turn off the power
immediately and have it repaired at a qualified service center.
Avoid using this product and all accessories outdoors.
Attention:
Place the WBR-6600 on a stable surface.
Only use the power adapter that comes with the package. Using a different voltage
rating power adaptor may damage the router.
Page 15
15
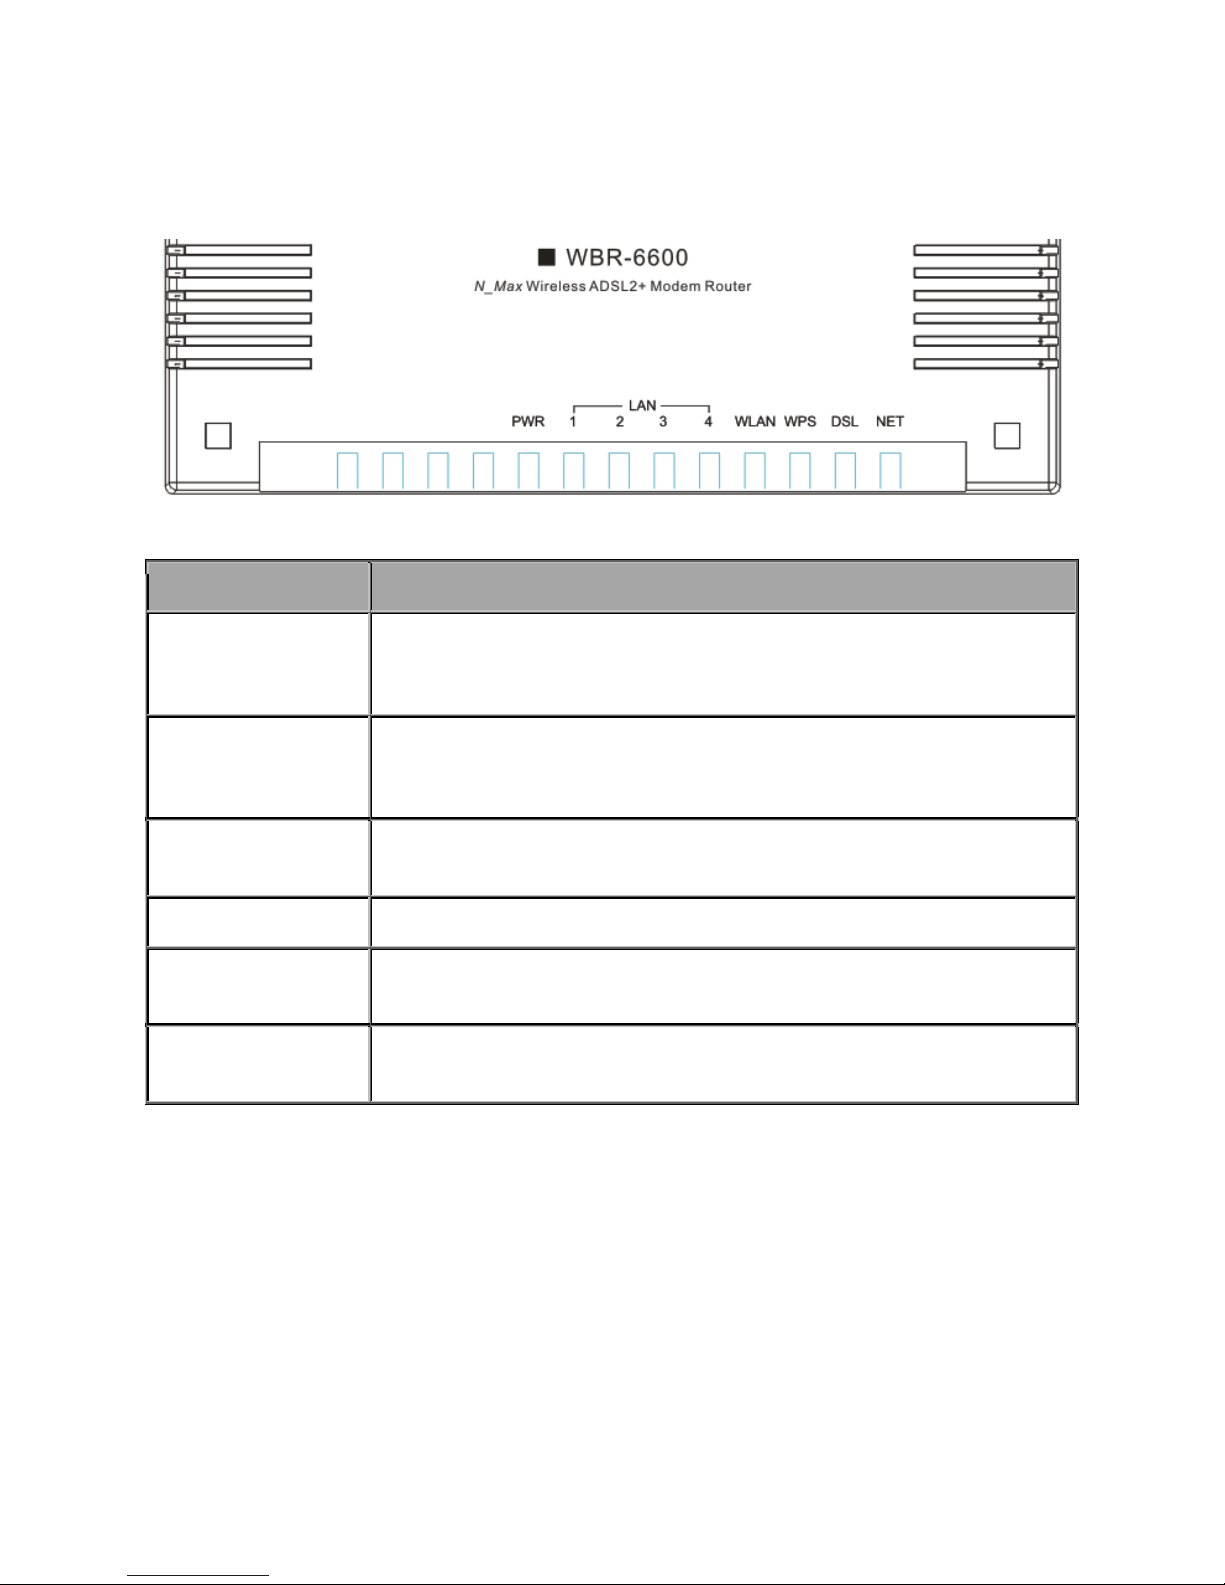
The Front LEDs - WBR-6600
LED
Meaning
Power:
When the power is plugged in, it will light Red and when the system is
ready, it will remain Green. Whilst the system is rebooting or firmware
upgrading, the LED light flashes.
LAN Ports 1-4:
Lights when connected to an Ethernet device.
Green for 100Mbps; Orange for 10Mbps.
Blinking when data is Transmitted / Received.
WLAN:
Lights green when the wireless connection is established.
Flashes when sending/receiving data.
WPS
Blinking when WiFi Protected Setup (WPS) is in progress.
DSL:
Remain lit when successfully connected to ADSL.
Linesync is achieved.
NET :
Lights red when WAN port fails to get IP address.
Lights green when WAN port gets IP address successfully.
Page 16
16
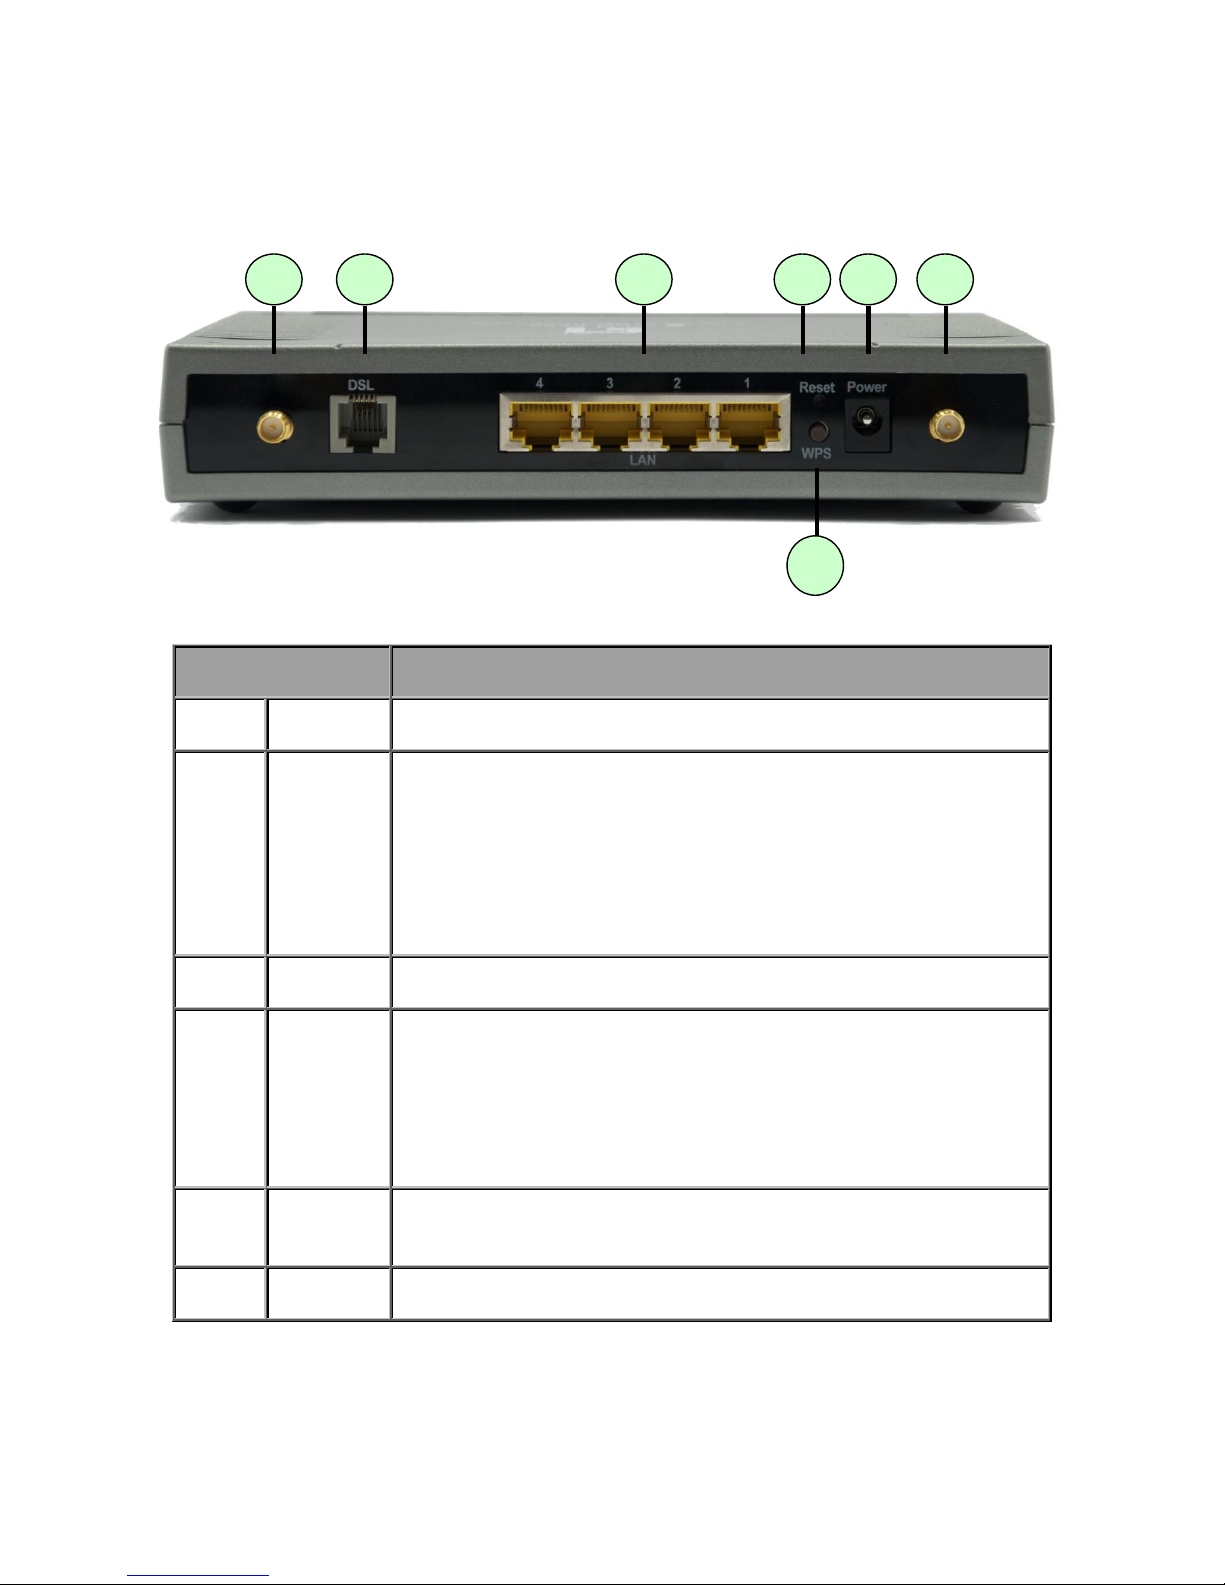
The Rear Ports - WBR-6600
Port
Description
1
Power
Connect the supplied power adapter to this jack.
2
Reset
After the router is powered on, press this reset button using the
end of paper clip or other small pointed object to reset the router
and to restore it to factory default settings.
1. Recovery procedures for non-working routers (e.g. after a
failed firmware upgrade flash).
2. Recovery procedures for a lost web interface password:
3
WPS
Push WPS button to trigger Wi-Fi Protected Setup function.
4
Ethernet
Connect a UTP Ethernet cable (Cat-5 or Cat-5e) to one of the
four LAN ports when connecting to a PC or an office/home
network of 10Mbps or 100Mbps.
Note: Only Ethernet port 1 can be used for EWAN.
5
DSL
Connect the supplied RJ-11 (“telephone”) cable to this port when
connecting to the ADSL/telephone network.
6
Antenna
Connect the detachable antenna to this port.
3
Page 17
17
The detail instruction in Reset Button
Recovery procedures for non-working routers (e.g. after a failed firmware upgrade flash):
Hold the Reset Button on the back of the modem in. Keep this button held in and turn on the
modem. Once the lights on the modem have stopped flashing, release the Reset Button.
The modem's emergency-reflash web interface will then be accessible via http://192.168.0.1
where you can upload a firmware image to restore the modem to a functional state. Please
note that the modem will only respond via its web interface at this address, and will not
respond to ping requests from your PC or to telnet connections.
Note:
Before powering on the router to enter the recovery process, please configure the IP
address of the PC as 192.168.0.100 and proceed with the following step by step guide.
1. Power the router off.
2. Hold the "Reset Button”.
3. Power on the router. Then Router's IP will reset to Emergency IP address (Say
192.168.0.1)
4. Flash the firmware.
Page 18
18
Antenna Position Placement
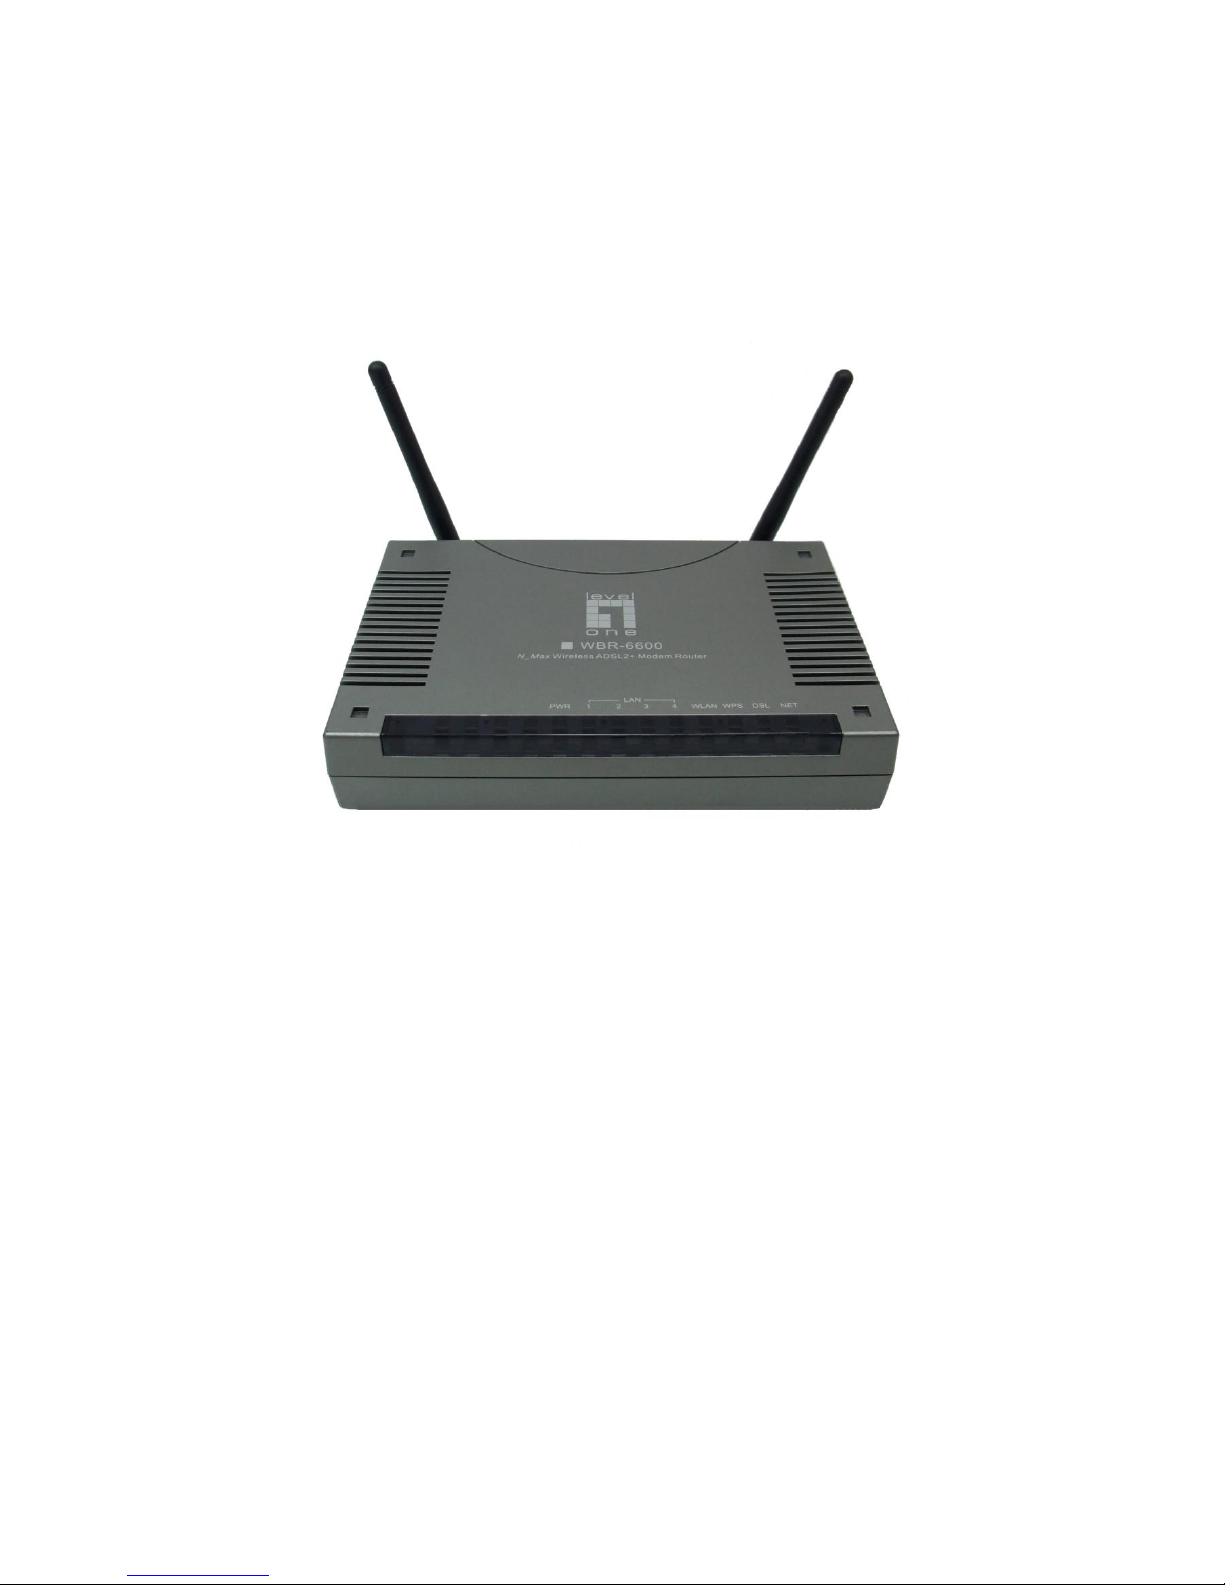
To get the best quality wireless reception out of your router, the antennas should be
positioned at 45 degree angles, like the following image, to minimize the wireless
interference caused between the antennas.
Cabling
One of the most common causes of problems is because of bad cabling or ADSL line(s).
Make sure that all connected devices are turned on. On the front of the product is a bank of
LEDs. Verify that the LAN Link and ADSL line LEDs are lit. If they are not, verify that you are
using the proper cables.
Ensure that all other devices connected to the same telephone line as your router (e.g.
telephones, fax machines, analogue modems) have a line filter connected between them
and the wall socket (unless you are using a Central Splitter or Central Filter installed by a
qualified and licensed electrician), and to ensure that all line filters are correctly installed and
the right way around. Missing line filters or line filters installed being the wrong way around
can cause problems with your ADSL connection, which includes frequent disconnections.
Page 19
19
Chapter 3 - Installation
You can configure the WBR-6600 router through the convenient and user-friendly interface
of a web browser. Most popular operating systems such as Linux, MAC OS and Windows
98/NT/2000/XP/Vista include a web browser as a standard application.
Before Configuration
PCs must have a properly installed Ethernet interface which connects to the router directly
or through an external repeater hub. In addition, PCs must have TCP/IP installed and
configured to obtain an IP address through a DHCP server or a fixed IP address that must be
in the same subnet as the router. The default IP address of the router is 192.168.0.1 and the
subnet mask is 255.255.255.0 (i.e. any attached PC must be in the same subnet, and have
an IP address in the range between 192.168.0.2 and 192.168.0.254). The easiest way is to
configure the PC is to obtain an IP address automatically from the router using DHCP. If you
encounter any problems accessing the router‟s web interface you are advised to uninstall
any kind of software firewall on your PCs, as they can cause problems when trying to access
the 192.168.0.1 IP address of the router.
Please follow the steps below for installation on your PC‟s network environment. First of all,
check your PC‟s network components. The TCP/IP protocol stack and Ethernet network
adapter must be installed. If not, please refer to your Windows-related or other operating
system manuals.
Note: Any TCP/IP capable workstation can be used to communicate with or through the
WBR-6600. To configure other types of workstations, please consult the manufacturer‟s
documentation.
Page 20
20
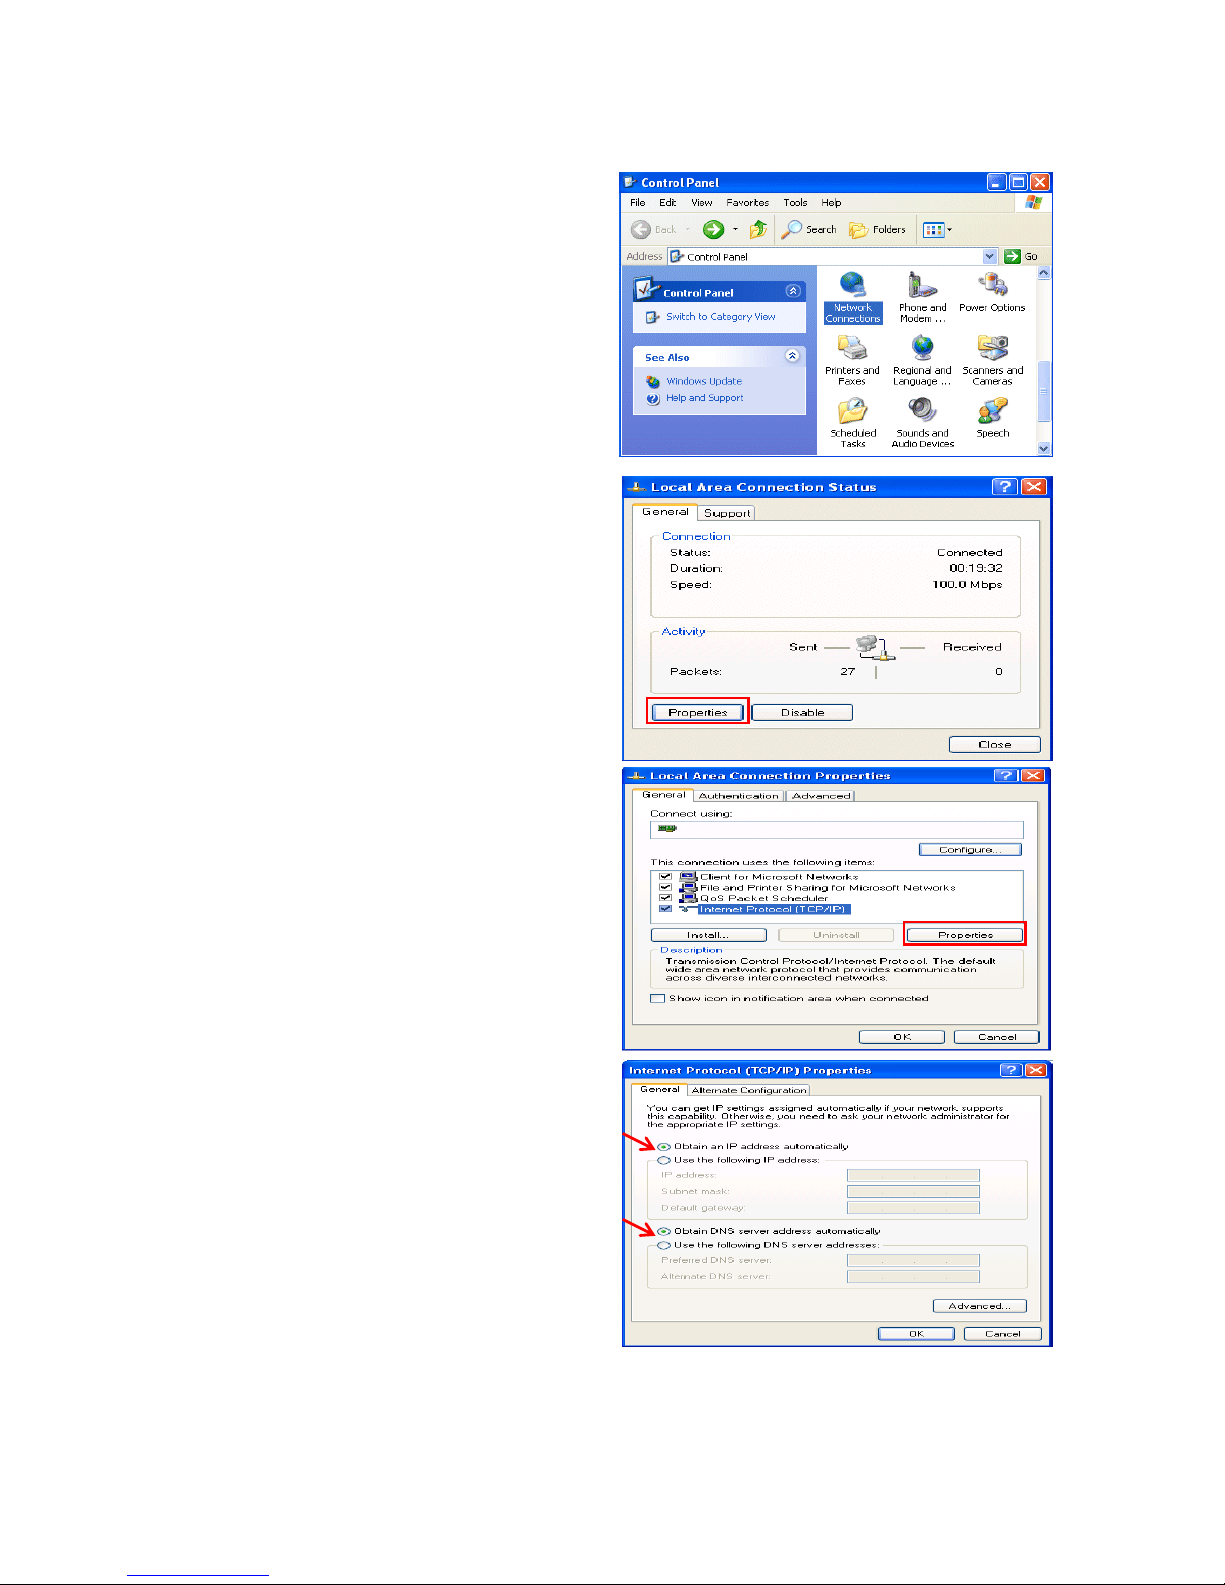
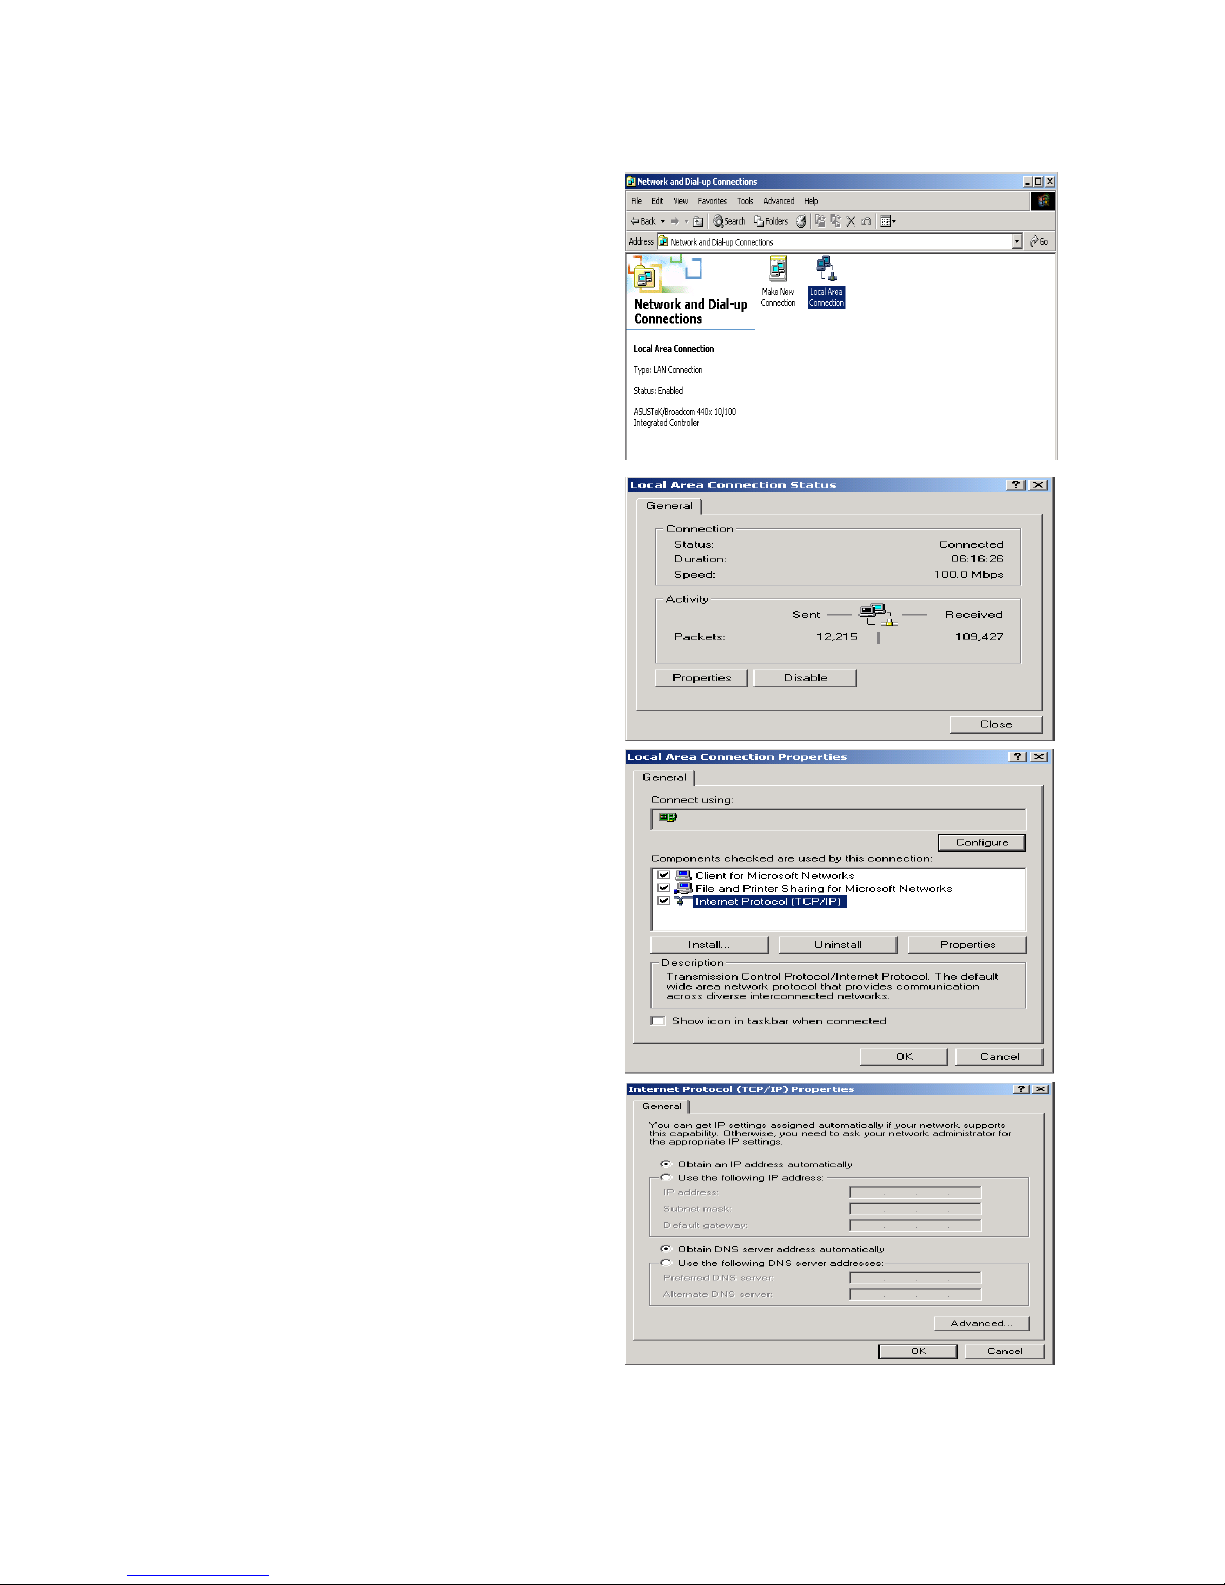
Configuring a PC in Windows XP
1. Go to Start / Control Panel (in
Classic View). In the Control Panel,
double-click on Network
Connections
2. Double-click Local Area Connection.
3. In the Local Area Connection Status
window, click Properties.
4. Select Internet Protocol (TCP/IP)
and click Properties.
5. Select the Obtain an IP address
automatically and the Obtain DNS
server address automatically radio
buttons.
6. Click OK to finish the configuration.
Page 21
21
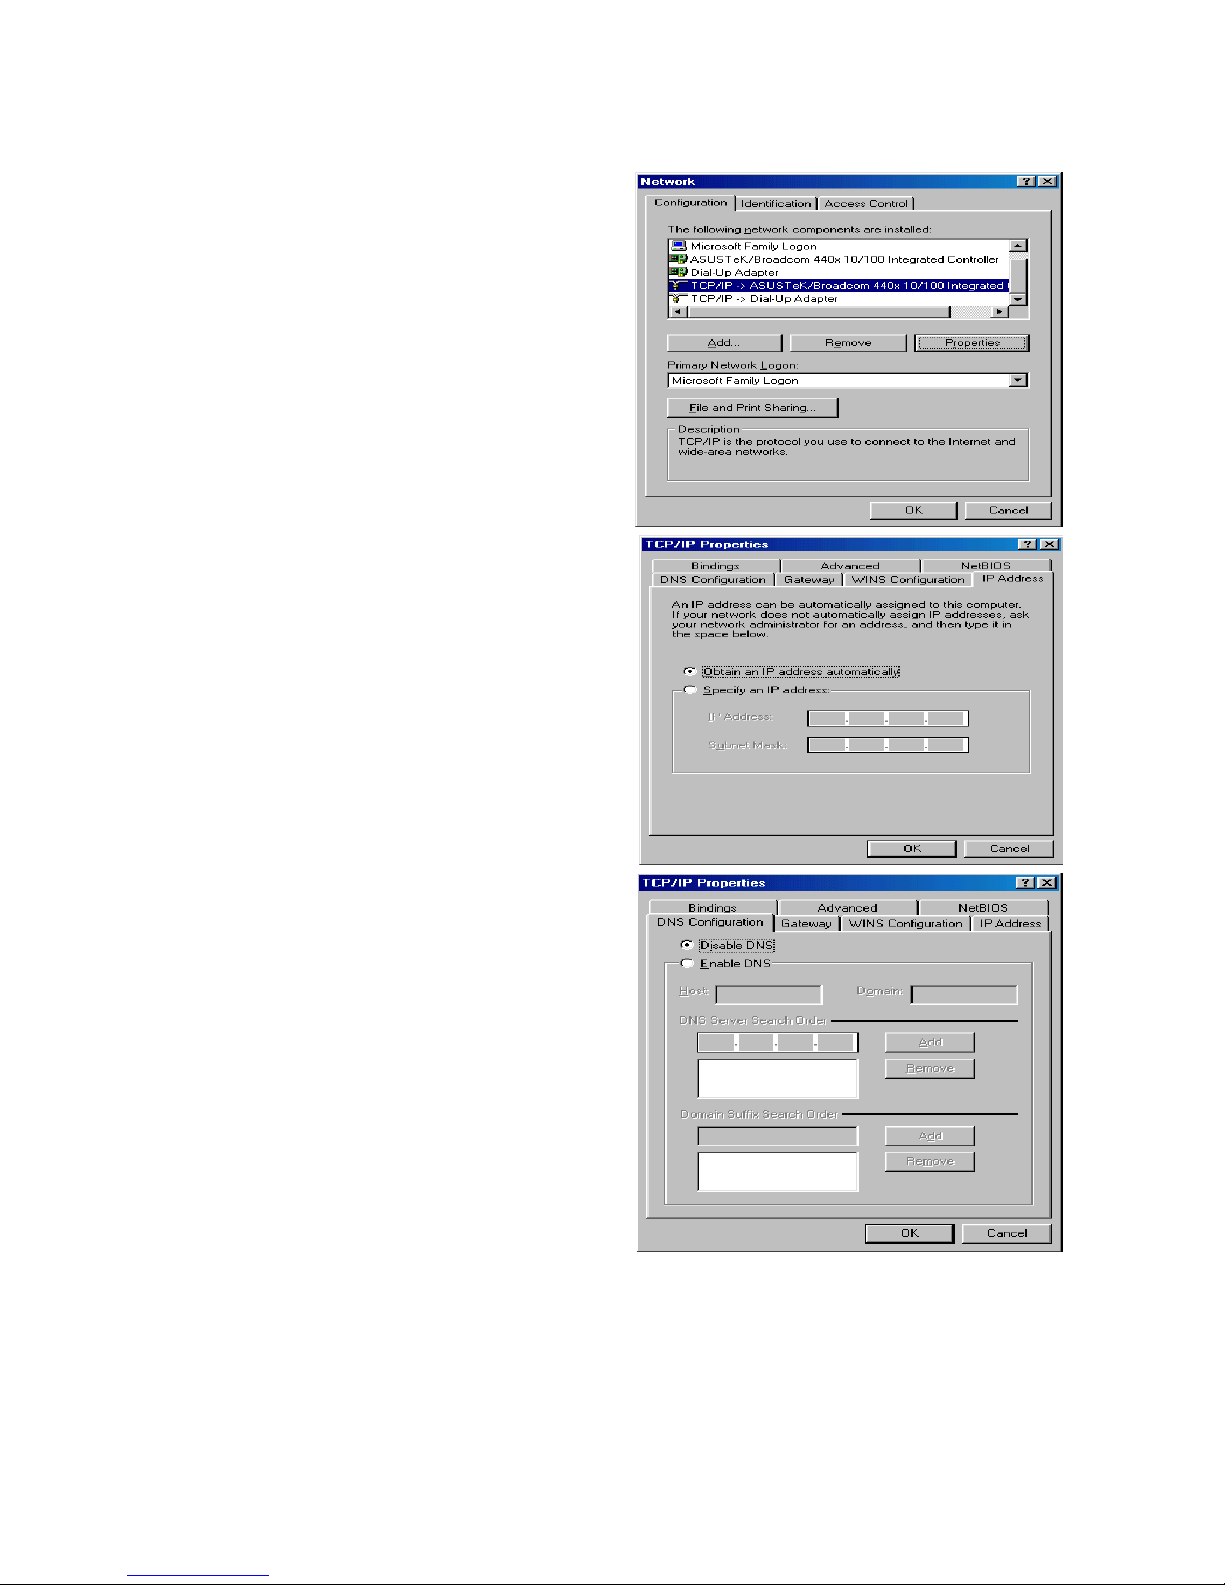
Configuring a PC in Windows 2000
1. Go to Start / Settings / Control Panel.
In the Control Panel, double-click on
Network and Dial-up Connections.
2. Double-click Local Area Connection.
3. In the Local Area Connection Status
window click Properties.
4. Select Internet Protocol (TCP/IP) and
click Properties.
5. Select the Obtain an IP address
automatically and the Obtain DNS
server address automatically radio
buttons.
6. Click OK to finish the configuration.
Page 22
22
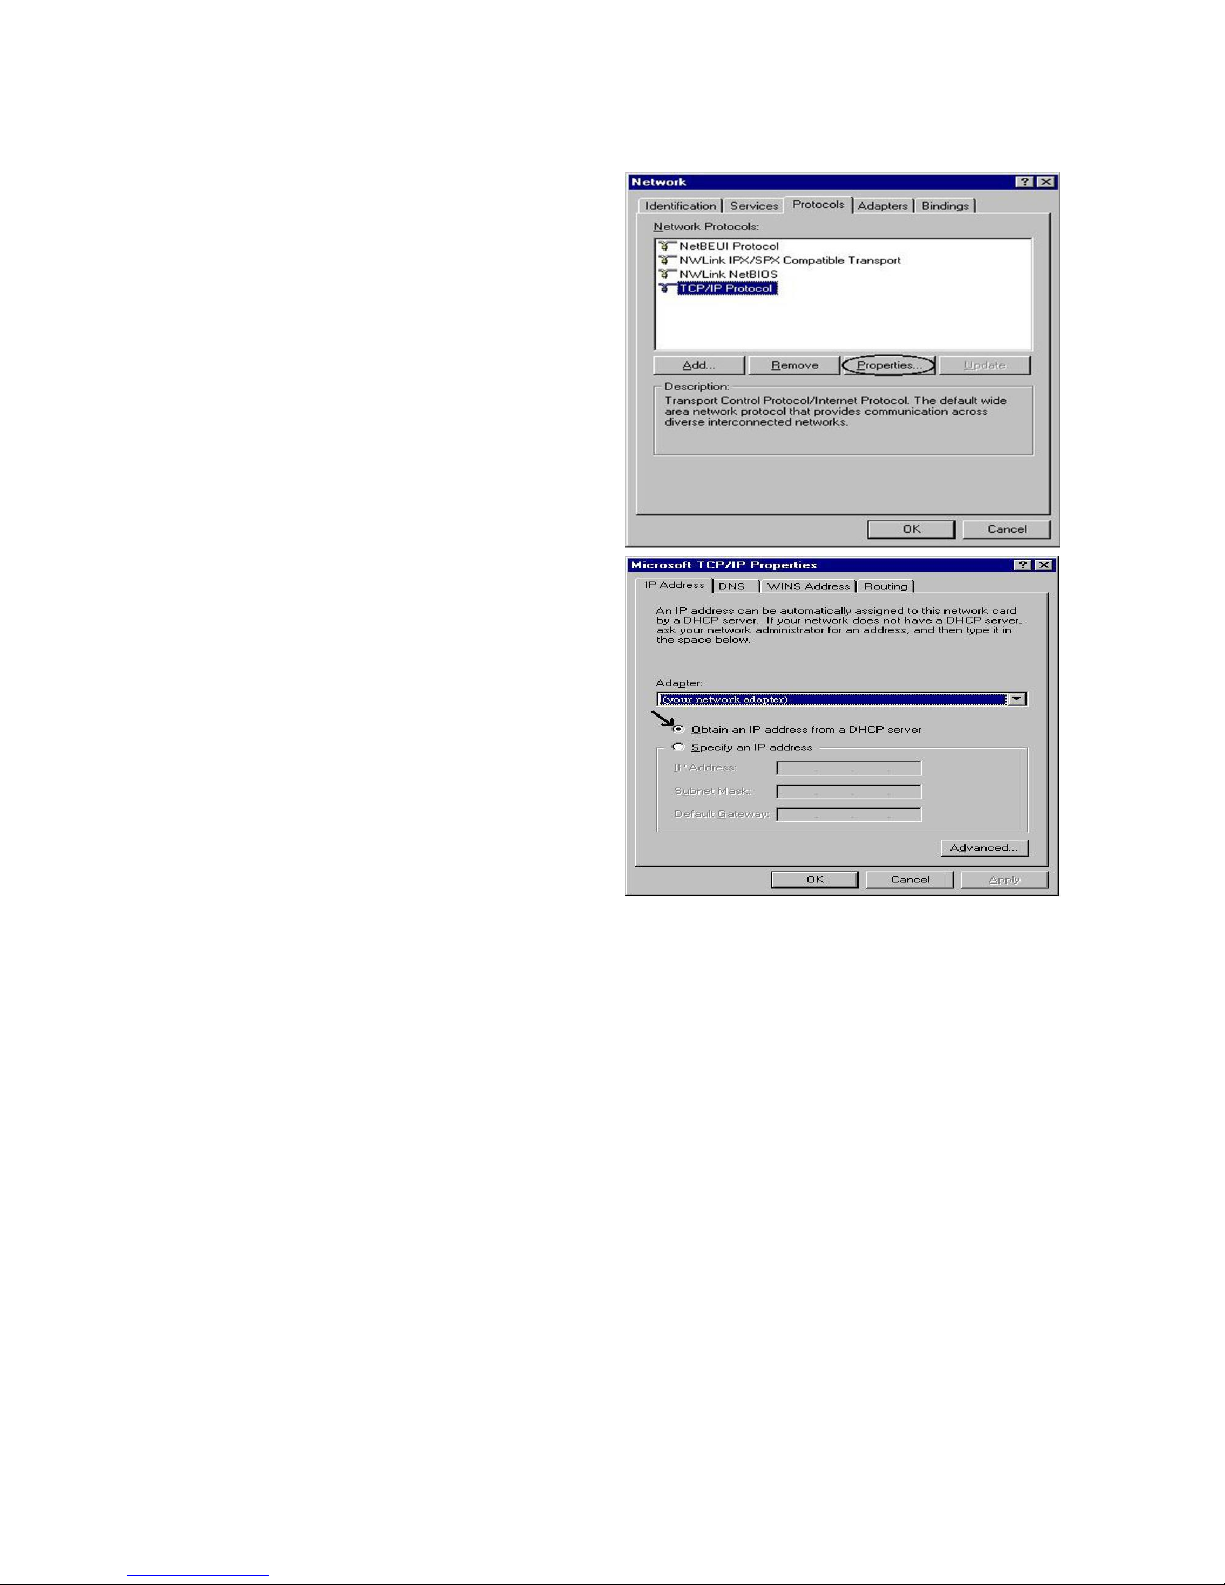
Configuring PC in Windows 98/Me
1. Go to Start / Settings / Control Panel.
In the Control Panel, double-click on
Network and choose the
Configuration tab.
2. Select TCP/IP, or the name of your
Network Interface Card (NIC) in your
PC.
3. Select the Obtain an IP address
automatically radio button.
4. Then select the DNS Configuration
tab.
5. Select the Disable DNS radio button
and click OK to finish the configuration.
Page 23
23
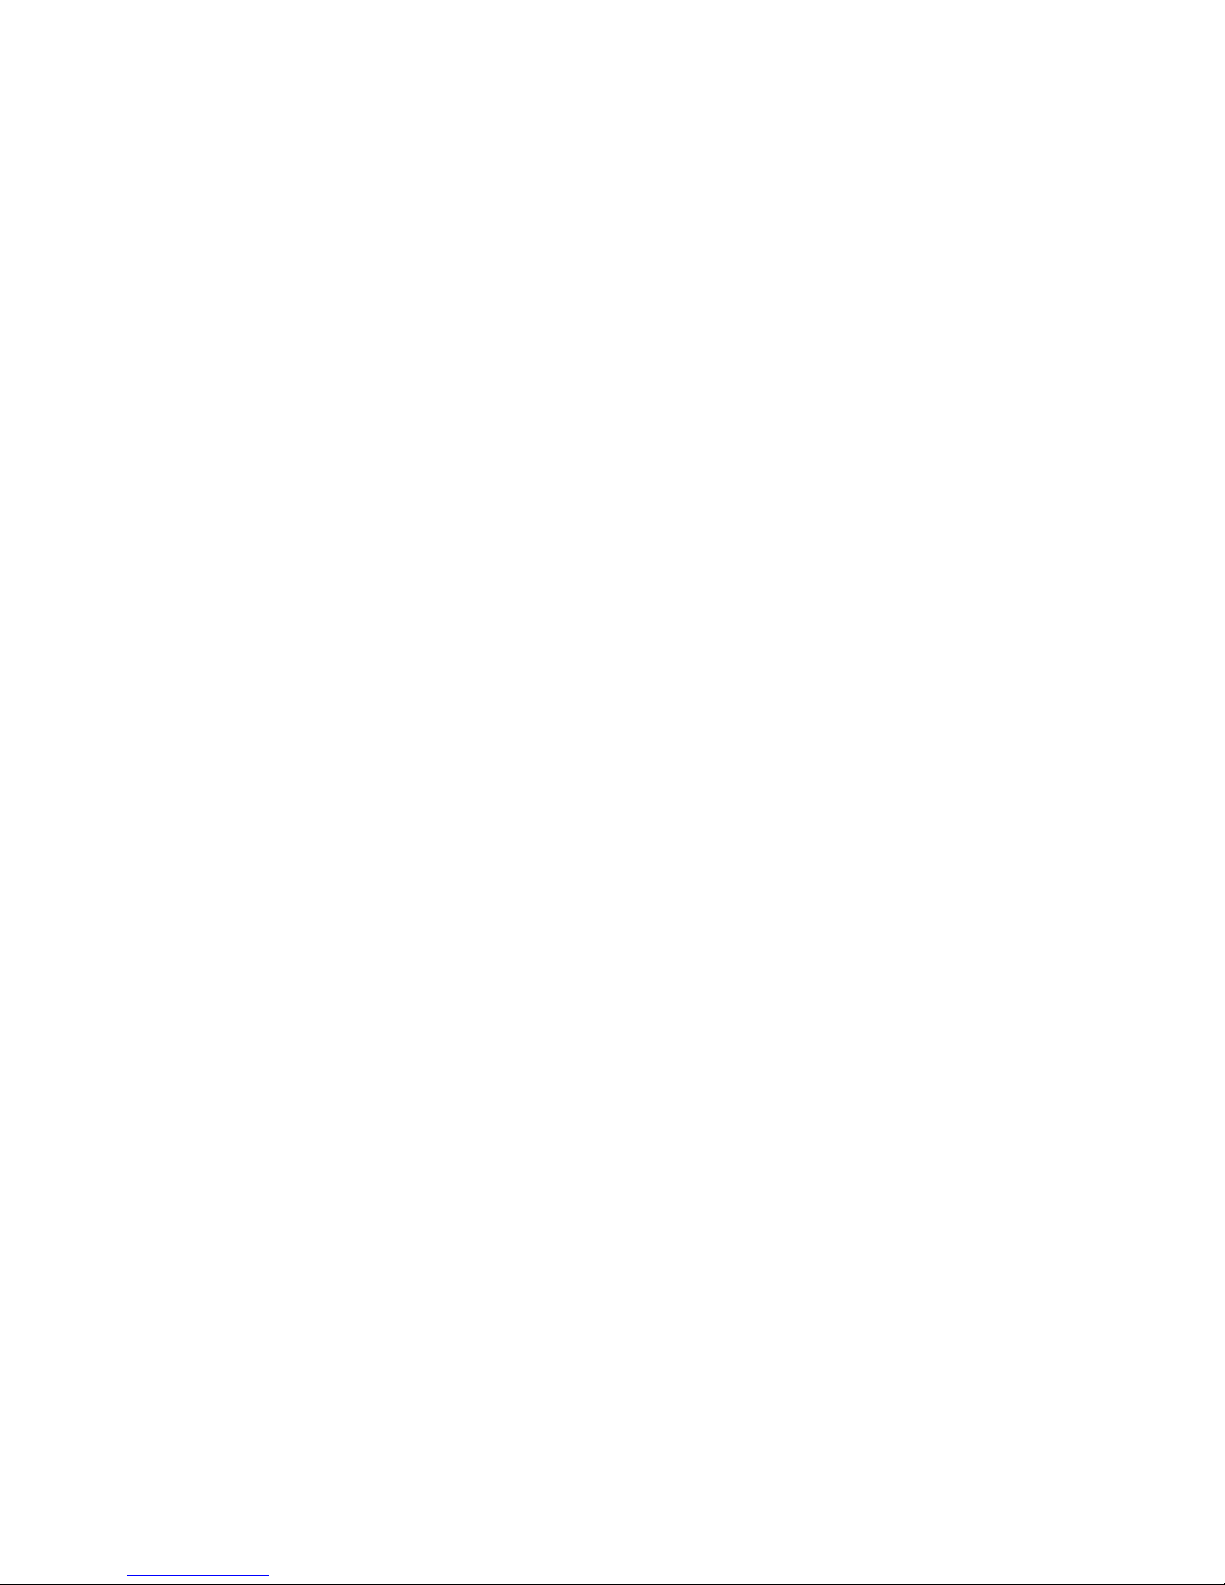
Configuring PC in Windows NT4.0
1. Go to Start / Settings / Control Panel.
In the Control Panel, double-click on
Network and choose the Protocols tab.
2. Select TCP/IP Protocol and click
Properties.
3. Select the Obtain an IP address from a
DHCP server radio button and click OK.
Page 24
24
Factory Default Settings
Before configuring the WBR-6600 router, you need to know the following default settings.
Web Interface: (Username and Password)
Username: admin
Password: password
The default username and password are “admin” and “password” respectively.
Attention:
If you ever forget the username/password to login to the router, you may press the RESET
button up to 6 seconds then release it to restore the factory default settings.
Caution: After pressing the RESET button for more than 6 seconds then release it, to be sure you power cycle
the device again.
LAN Device IP Settings:
IP Address: 192.168.0.1
Subnet Mask: 255.255.255.0
ISP setting in WAN site:
PPPoE
DHCP Server:
DHCP server is enabled.
Start IP Address: 192.168.0.2
IP pool counts: 253
Page 25
25
LAN and WAN Port Addresses
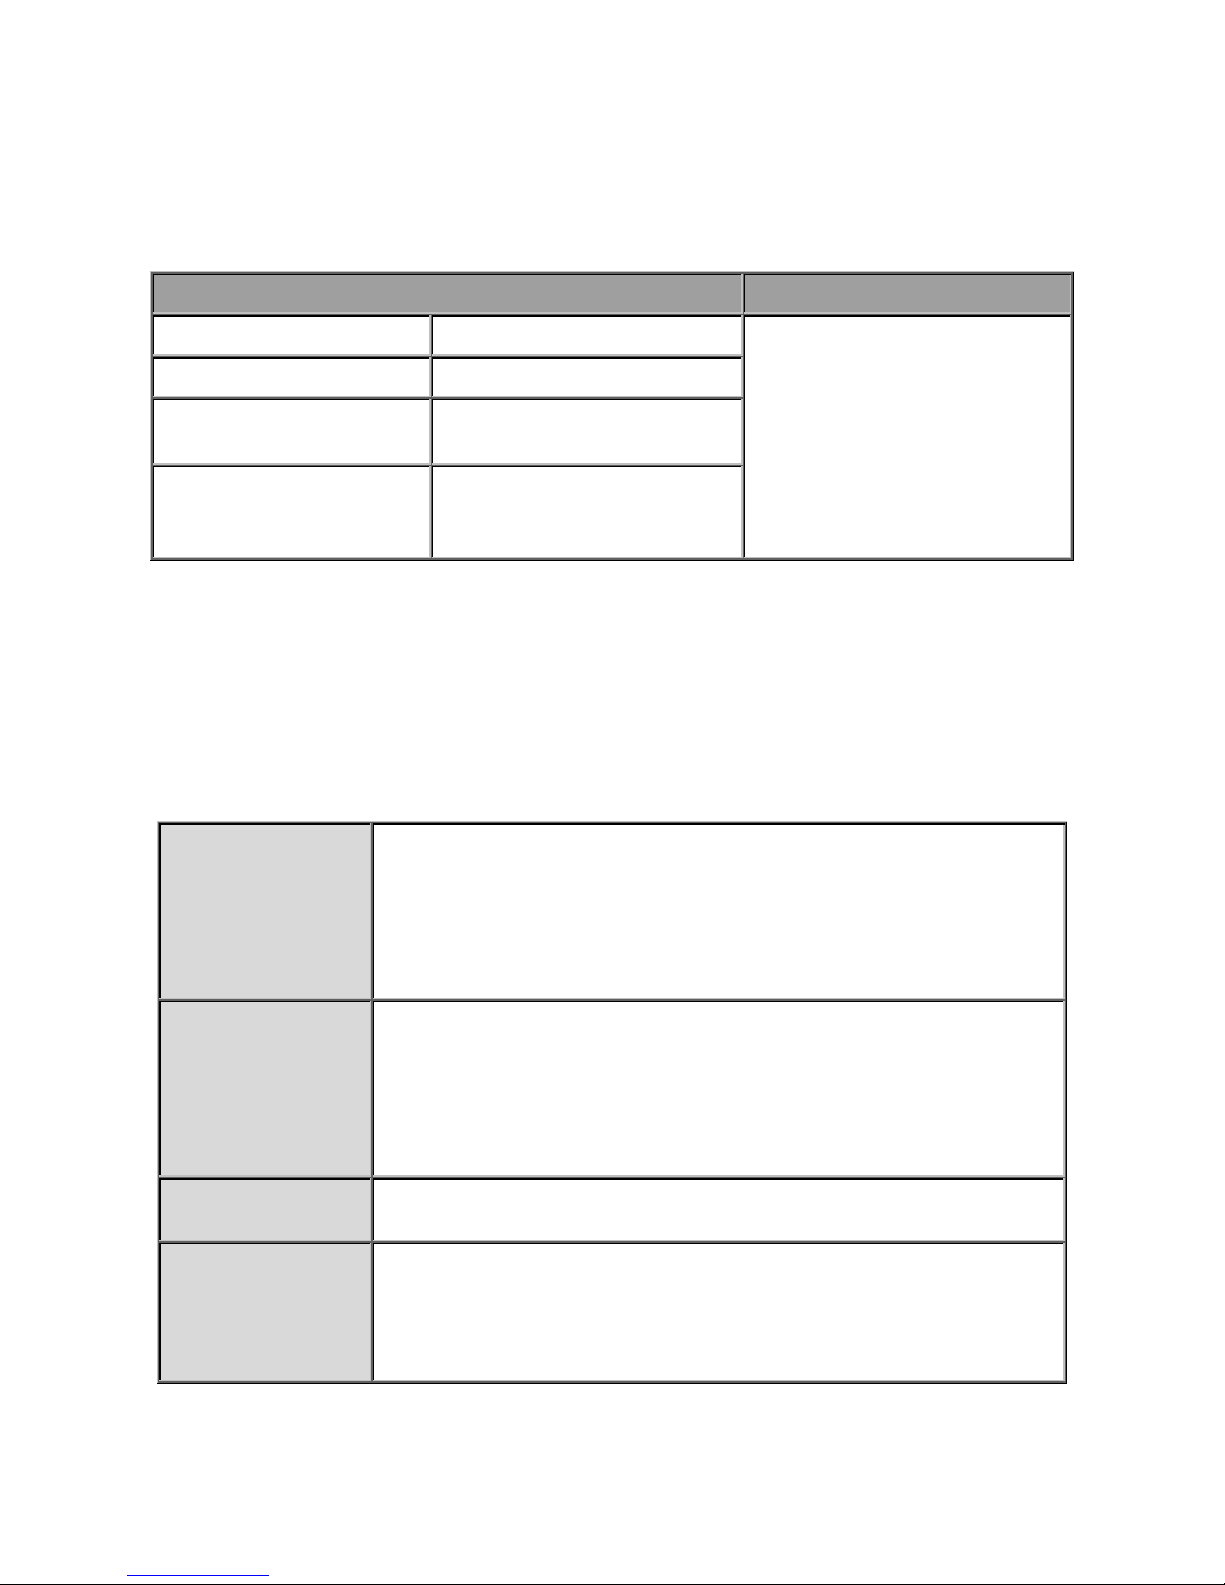
The parameters of LAN and WAN ports are preset at the factory. The default values are
shown below.
LAN Port
WAN Port
IP address
192.168.0.1
The PPPoE function is enabled
to automatically get the WAN
port configuration from the ISP,
but you have to set the
username and password first.
Subnet Mask
255.255.255.0
DHCP server function
Enabled in ports 1, 2, 3, and
4
IP addresses for
distribution to PCs
253 IP addresses continuing
from 192.168.0.2 through
192.168.0.254
Information from your ISP
Before configuring this device, you have to check with your ISP (Internet Service Provider)
what kind of services are provided, such as PPPoE, PPPoA, MPoA or Pure Bridge.
Gather the information as illustrated in the following table and keep it for reference.
PPPoE
VPI/VCI, VC-based/LLC-based multiplexing, Username, Password,
Service Name, and Domain Name System (DNS) IP address (it can
be automatically assigned by your ISP when you connect or be set
manually).
PPPoA
VPI/VCI, VC-based/LLC-based multiplexing, Username, Password,
and Domain Name System (DNS) IP address (it can be
automatically assigned by your ISP when you connect or be set
manually).
RFC1483 Bridged
VPI/VCI, VC-based/LLC-based multiplexing to use Bridged Mode.
RFC1483 Routed
VPI/VCI, VC-based/LLC-based multiplexing, IP address, Subnet
mask, Gateway address, and Domain Name System (DNS) IP
address (it is fixed IP address).
Page 26
26
Configuring with your WBR-6600
Note:
1. To configure this device, you must have Internet Explorer 5.0 / Netscape 4.5 or above
installed
2. You may configure the router for Internet access in two ways:
(A) Easy Sign On (B) Web Configuration
Easy Sign On:
After setting up the router with the appropriate cables plugged, proceed to load your internet
browser.
Easy Sign On will start automatically once you open your Web Browser.
Follow the Easy Sign On Wizard and it will guide you to complete the basic network
configuration.
Note:
If Easy Sign-On does not start, please type in the address http://192.168.0.1, enter
Username and Password and click Quick Start. The Quick Start process is the same as
Easy Sign-On.
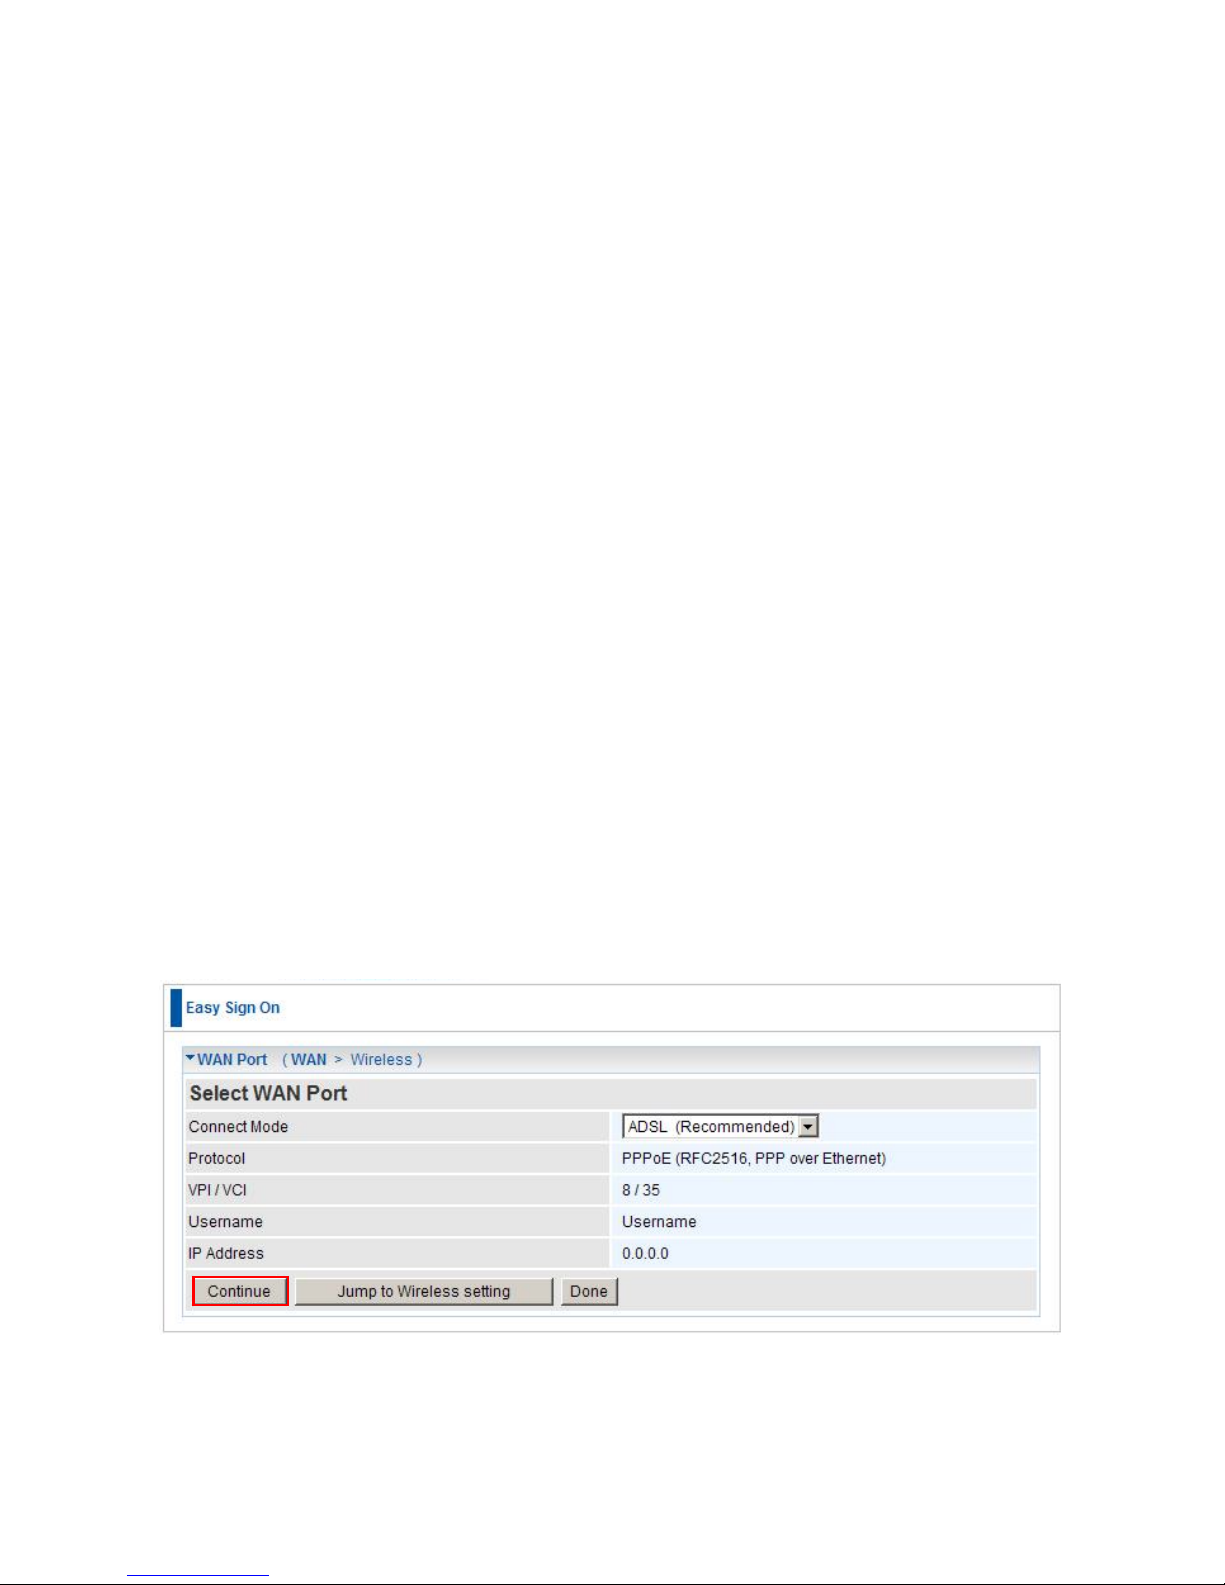
1. Click Continue.
Page 27
27
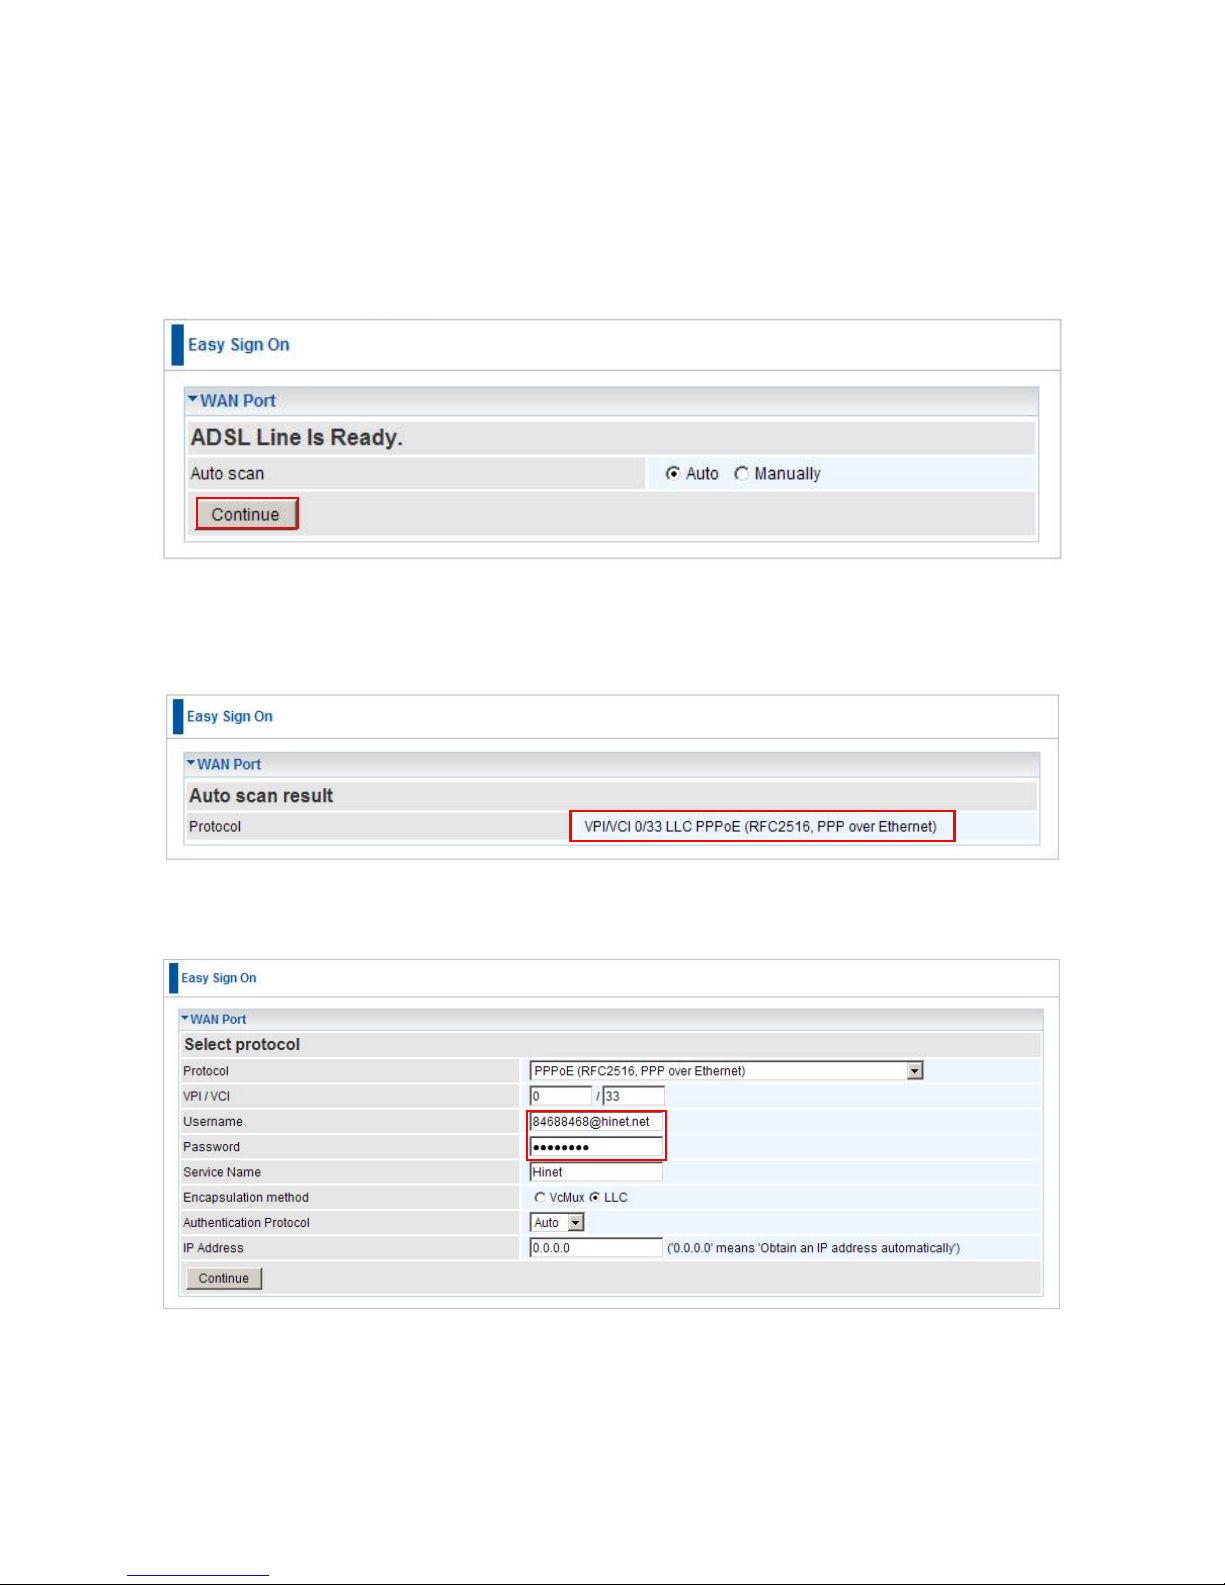
2. Choose “Auto” or “Manually” to scan ADSL settings.
Note:
If automatic detection does not work, please ask your ISP and enter the Protocol, VPI and
VCI manually.
3. The Auto scan result is displayed. Please note this may vary depending on your local
operator settings. If you are not sure, please consult your ISP (Internet Service Provider).
4. Please enter “Username” and “Password” as supplied by your ISP and click continue.
Page 28
28
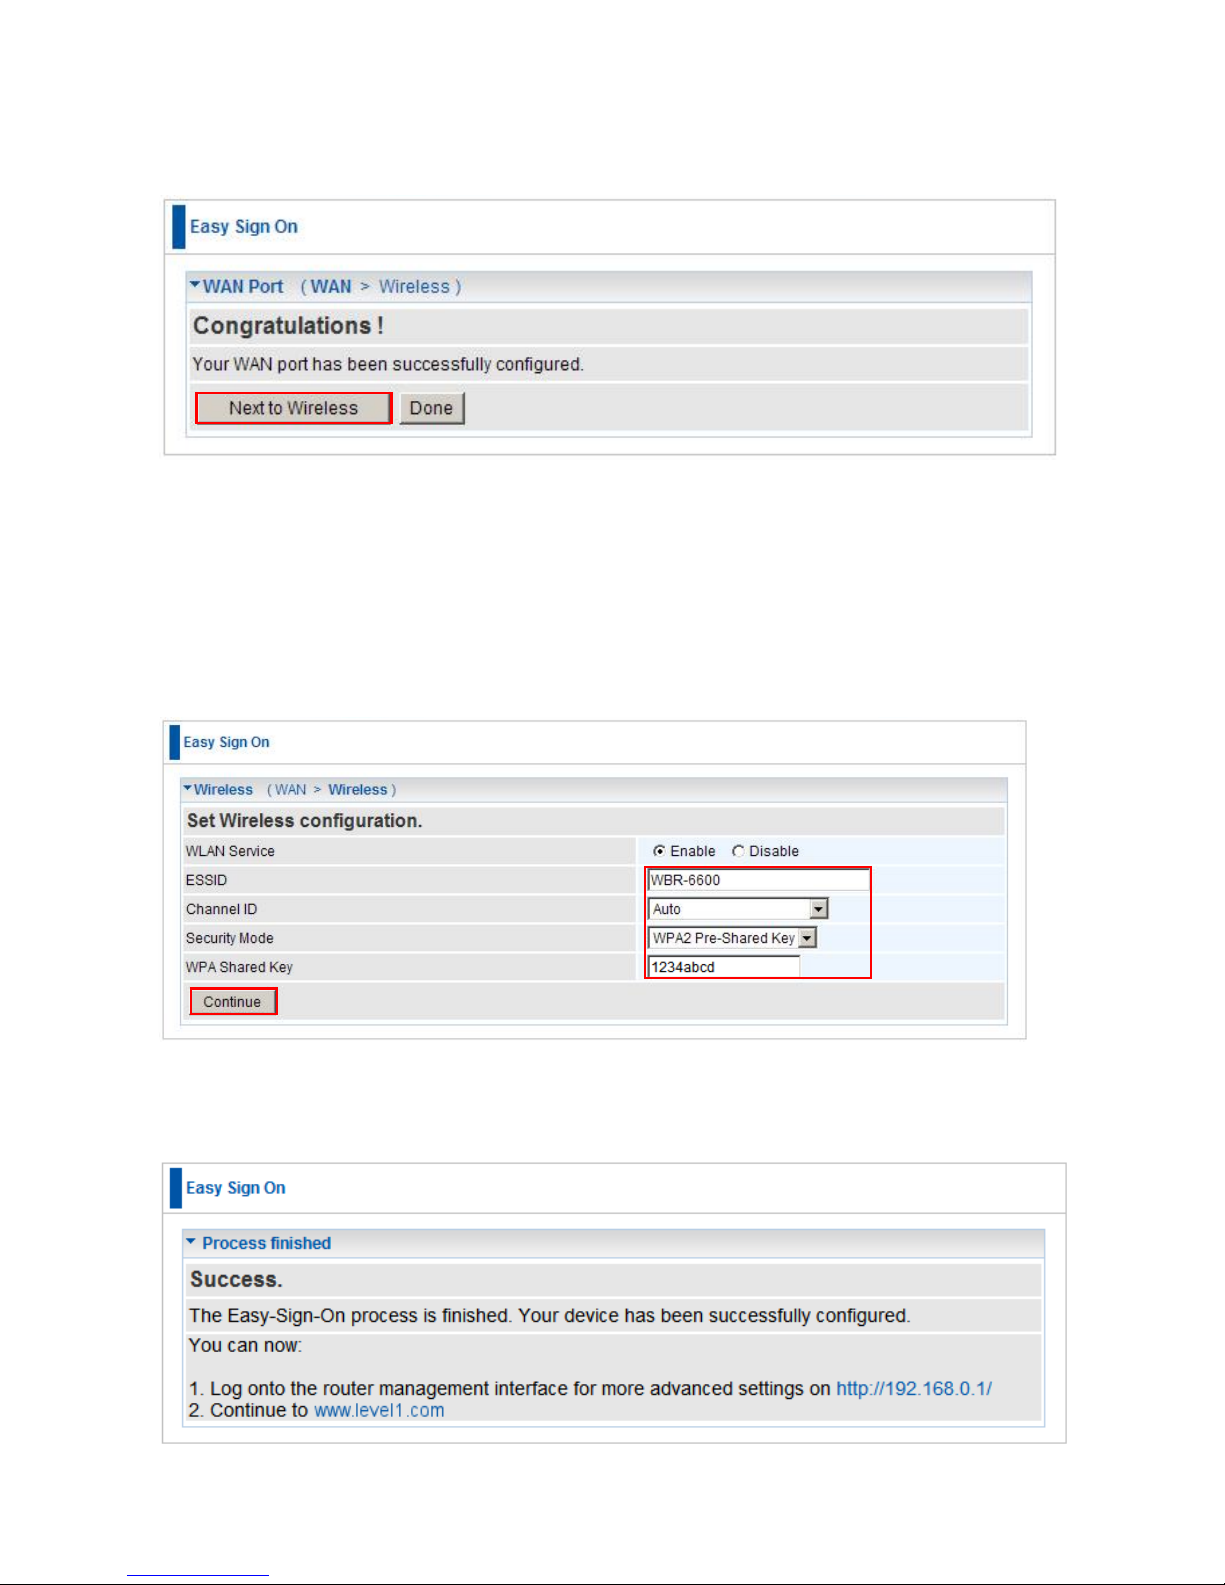
5. Internet Settings are Complete. Now proceed to wireless network settings.
6. LevelOne recommends WPA2 for maximum security.
The shared key is the passkey to your wireless network. It can be numbers or letters and
needs to be at least 8 characters.
Please ensure your wireless computers and devices are set to the same security mode
and key as the WBR-6600.
7. Congratulations!! You‟ve completed the setup procedure and you are now ready to surf
the Internet.
Page 29
29
Web Configuration:
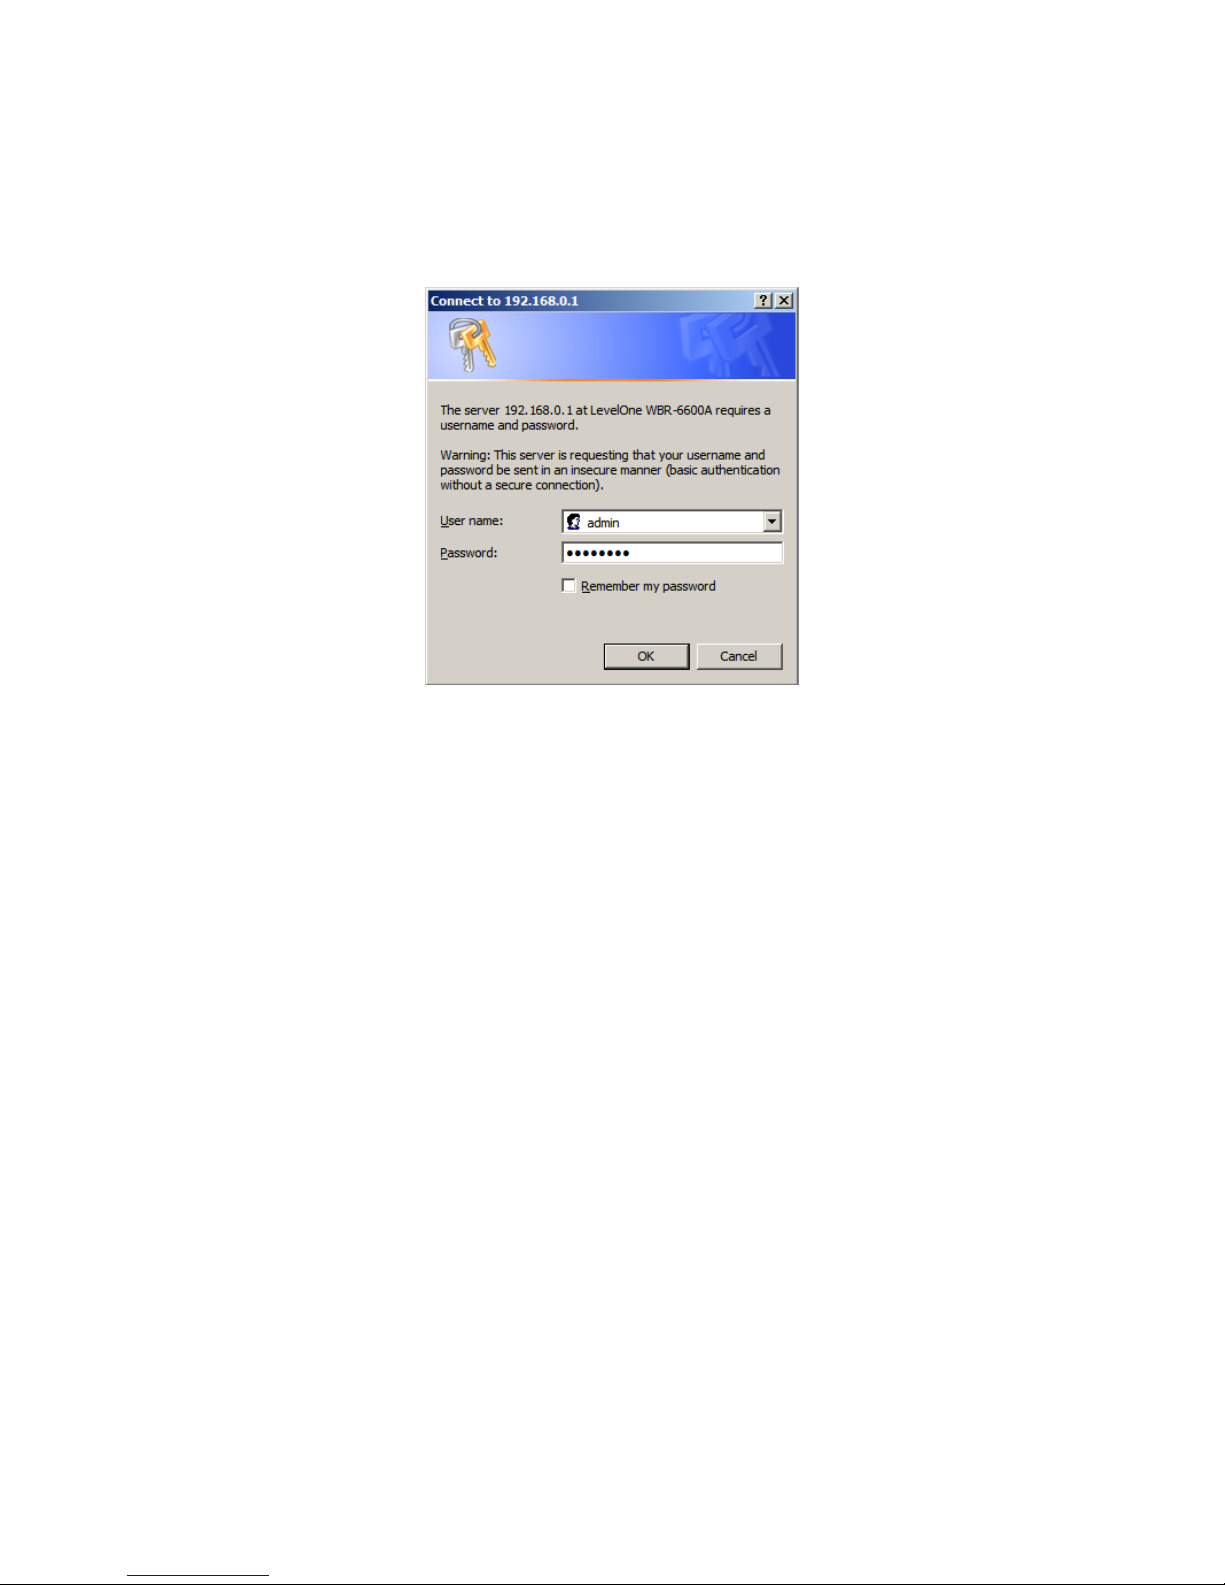
Open your web browser, enter the IP address of your router, which by default is 192.168.0.1,
and press the “Enter” key, a user name and password window prompt appears. The default
username and password are “admin” and “password”.
Congratulations! You have successfully logged on to your WBR-6600 Modem Router!
Page 30
30
Chapter 4 – Basic Configuration
Once you have logged on to your WBR-6600 Router via your web browser, you can begin to
set it up according to your requirements. On the configuration homepage, the left navigation
pane links you directly to the setup pages, which include:
Advance (Switch to Advance Configuration mode)
Status
Quick Start
WAN
WLAN
Page 31
31
Status Page
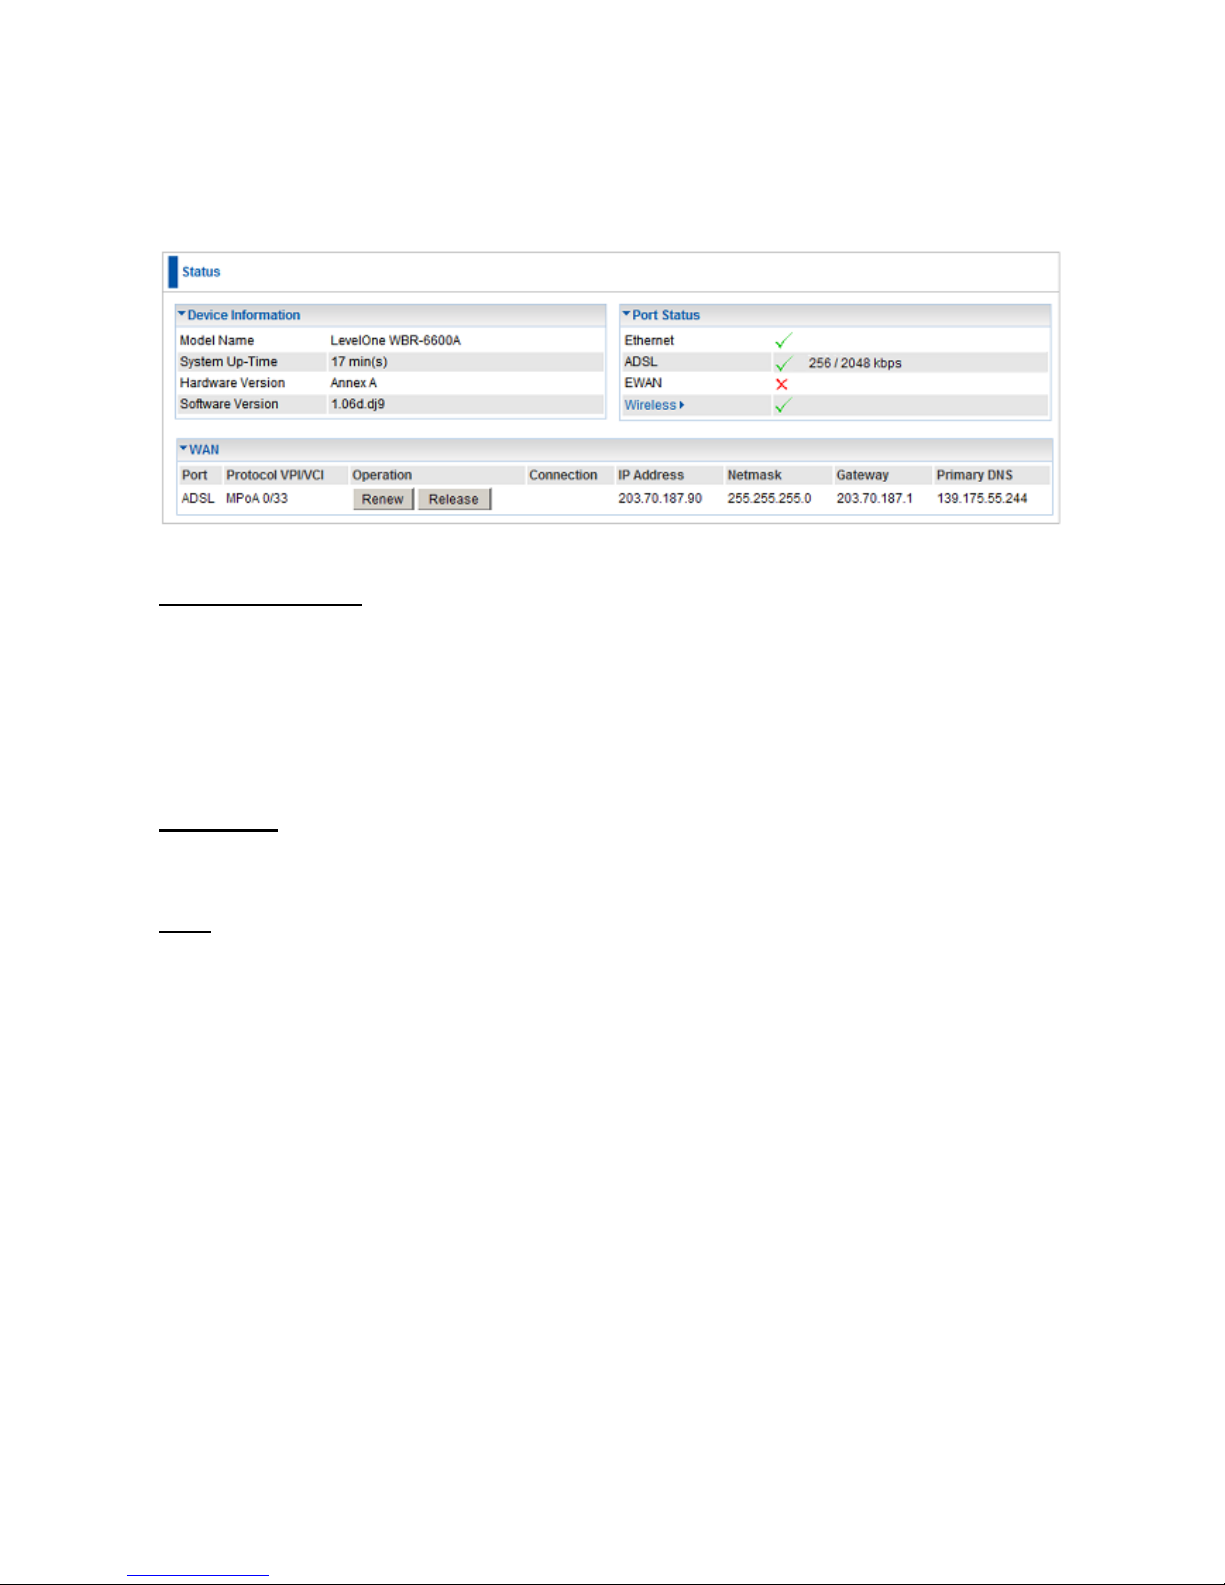
This page shows you the current status of the WBR-6600.
Device Information
Model Name: The model name of the device.
System Up-Time: Records system up-time.
Hardware Version: Device version
Software Version: Firmware version
Port Status
Port Status:User can look up to see if they are connected to Ethernet, ADSL.
WAN
Port: Name of the WAN connection.
Protocol VPI/VCI: Virtual Path Identifier and Virtual Channel Identifier
Operation: Current available operation.
Connection: The current connection status.
IP Address: WAN port IP address.
Netmask: WAN port IP subnet mask.
Gateway: The IP address of the default gateway.
Primary DNS: The IP address of the primary DNS server.
Page 32
32
Quick Start
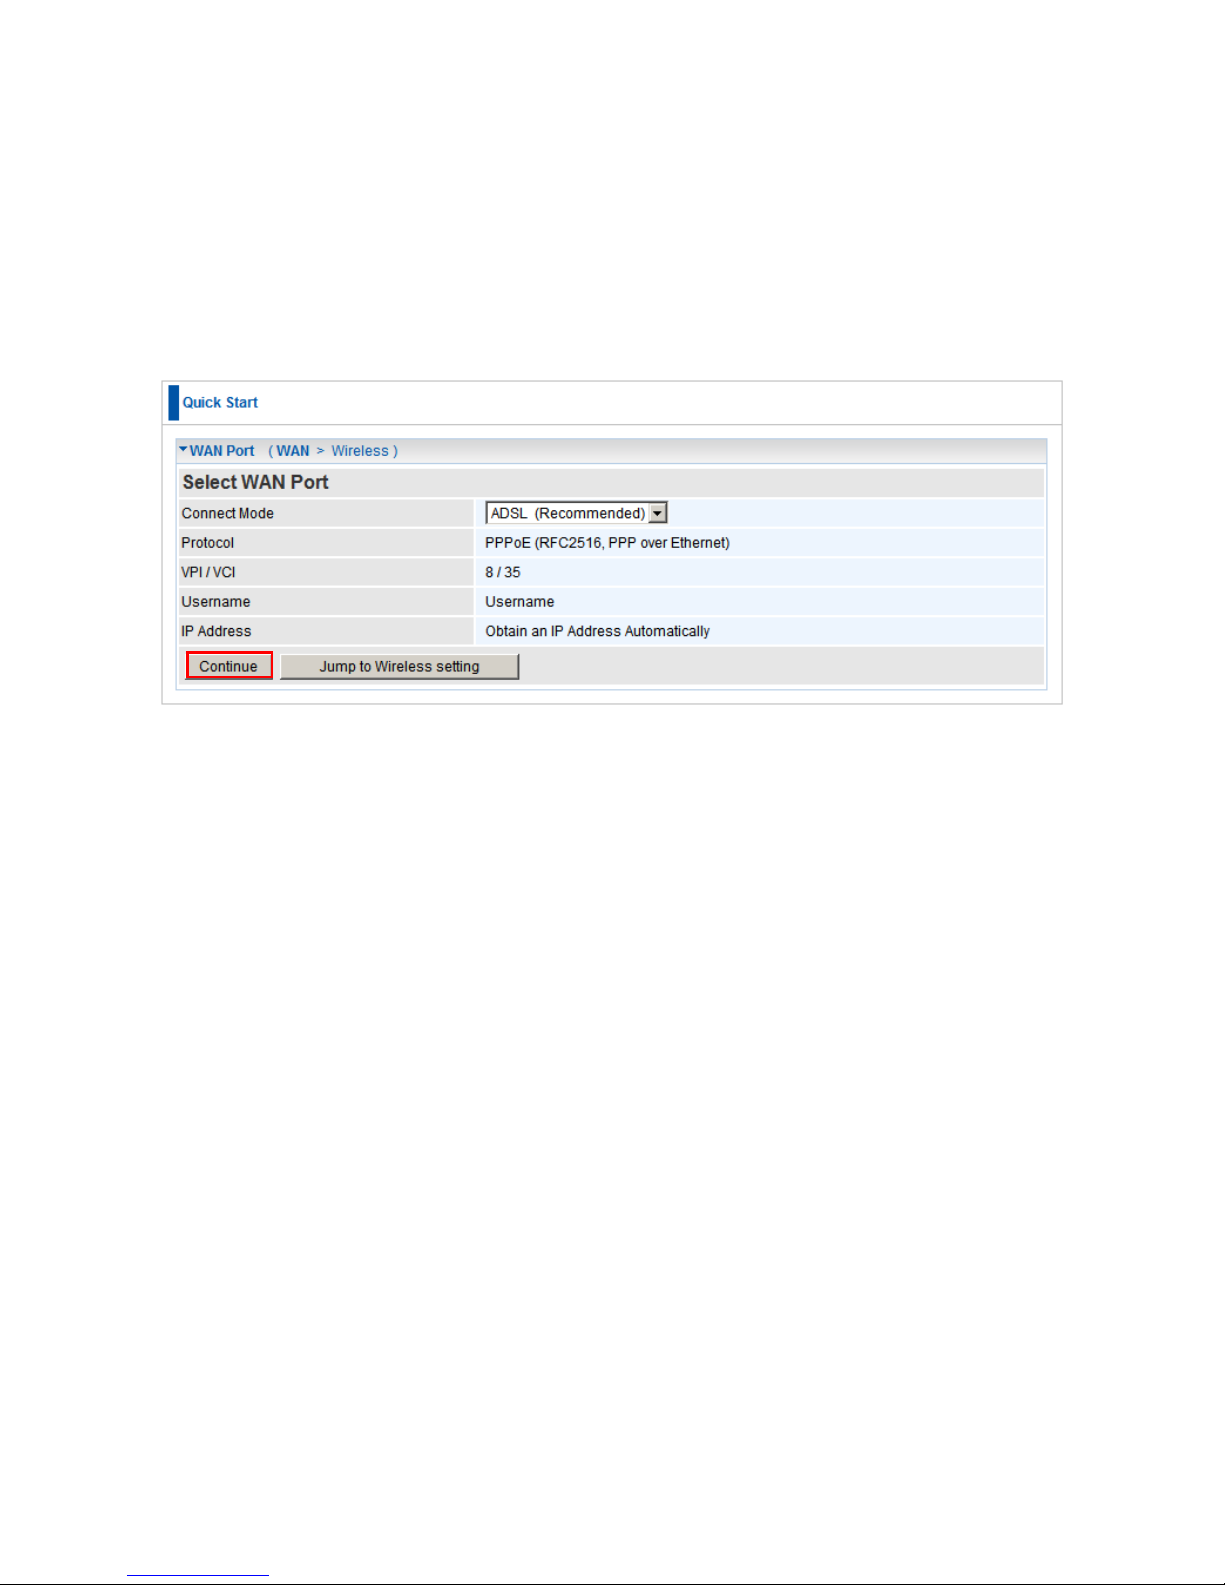
This wizard is similar to Easy Sign On, and will guide you through setting up your
WBR-6600.
Click Continue to start the wizard. The steps are the same as the Easy Sign On.
Page 33
33
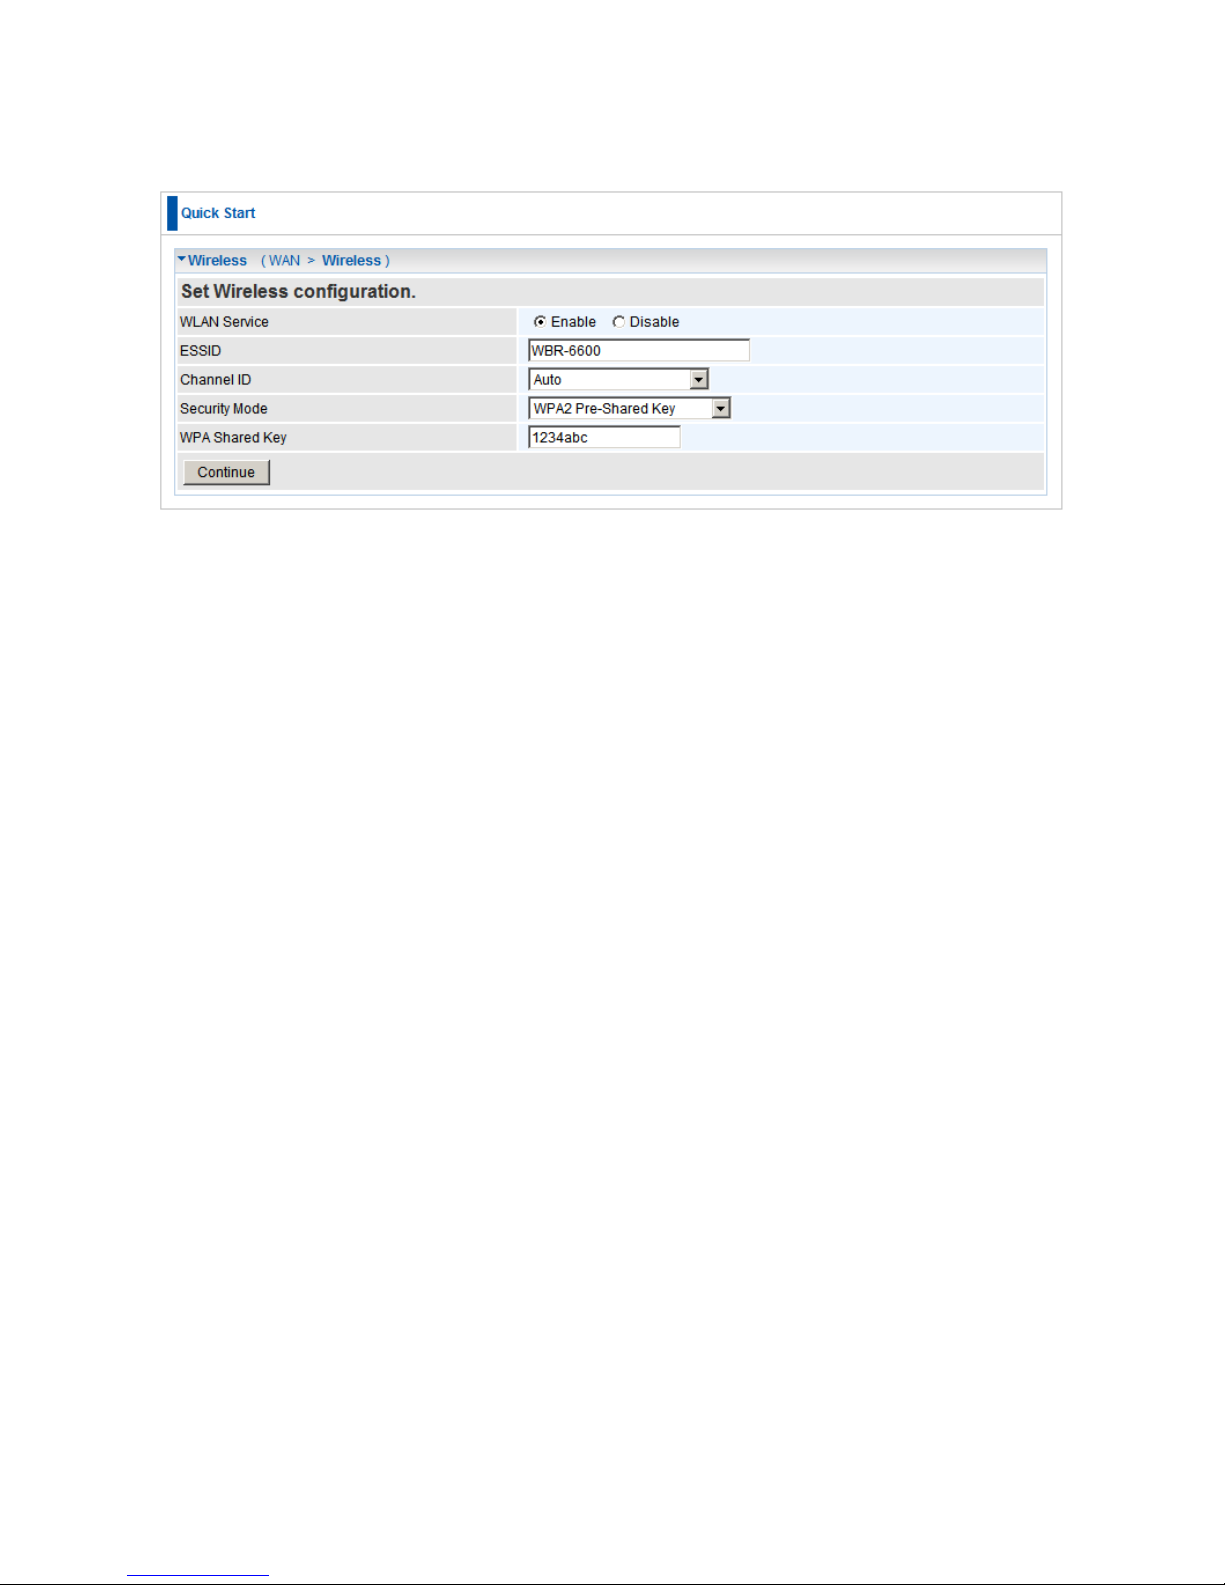
Set Wireless Configuration
WLAN Service: Default setting is set to Enable.
ESSID: The ESSID is the unique name of a wireless access point (AP) to be
distinguished from another. For security purpose, change to a unique ID name to the
AP which is already built-in to the router‟s wireless interface. It is case sensitive and
must not excess 32 characters. Make sure your wireless clients have exactly the
ESSID as the device, in order to get connected to your network.
Channel ID: Select the ID channel that you would like to use. (Recommend Auto)
Security Mode: You can disable or enable with WPA or WEP for protecting wireless
network. The default mode of wireless security is Disable.
Page 34
34
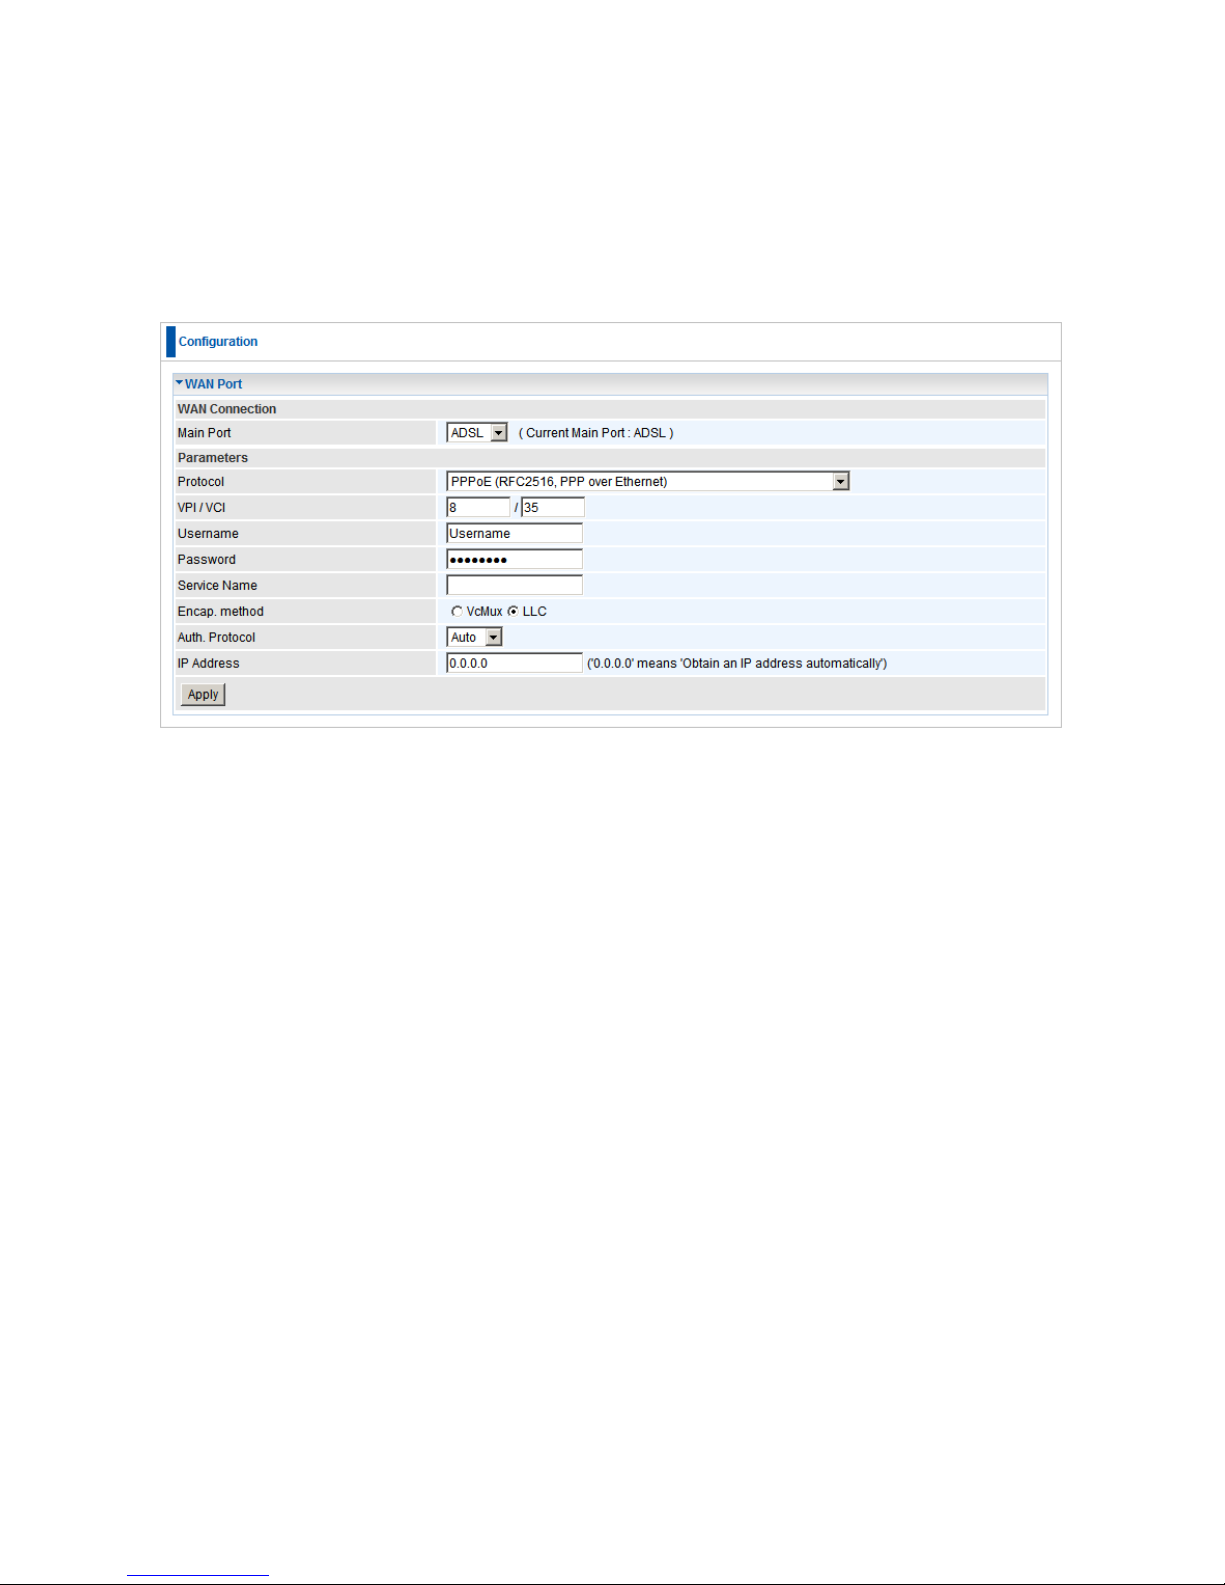
WAN
Here you can manually enter the ADSL settings provided by your Service Provider.
Use this if the Easy Sign On, or Quick Start cannot successfully auto-detect your ADSL
settings.
Main Port: To switch between ADSL and EWAN for WAN port function.
VPI/VCI: Enter the VPI and VCI information provided by your ISP.
Username: Enter the username provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive). This is in the format of “username@ispname”
instead of simply “username”.
Password: Enter the password provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive)
Service Name: This item is for identification purposes. If it is required, your ISP provides
you the information. Maximum input is 15 alphanumeric characters.
Encap. method: Select the encapsulation format, the default is LLC. Select the one
provided by your ISP
Auth. Protocol: Default is Auto. Your ISP advises on using Chap or Pap.
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Note: EWAN function turns LAN 1 into a WAN port. It supports DHCP, PPPoE or Static IP.
Page 35
35
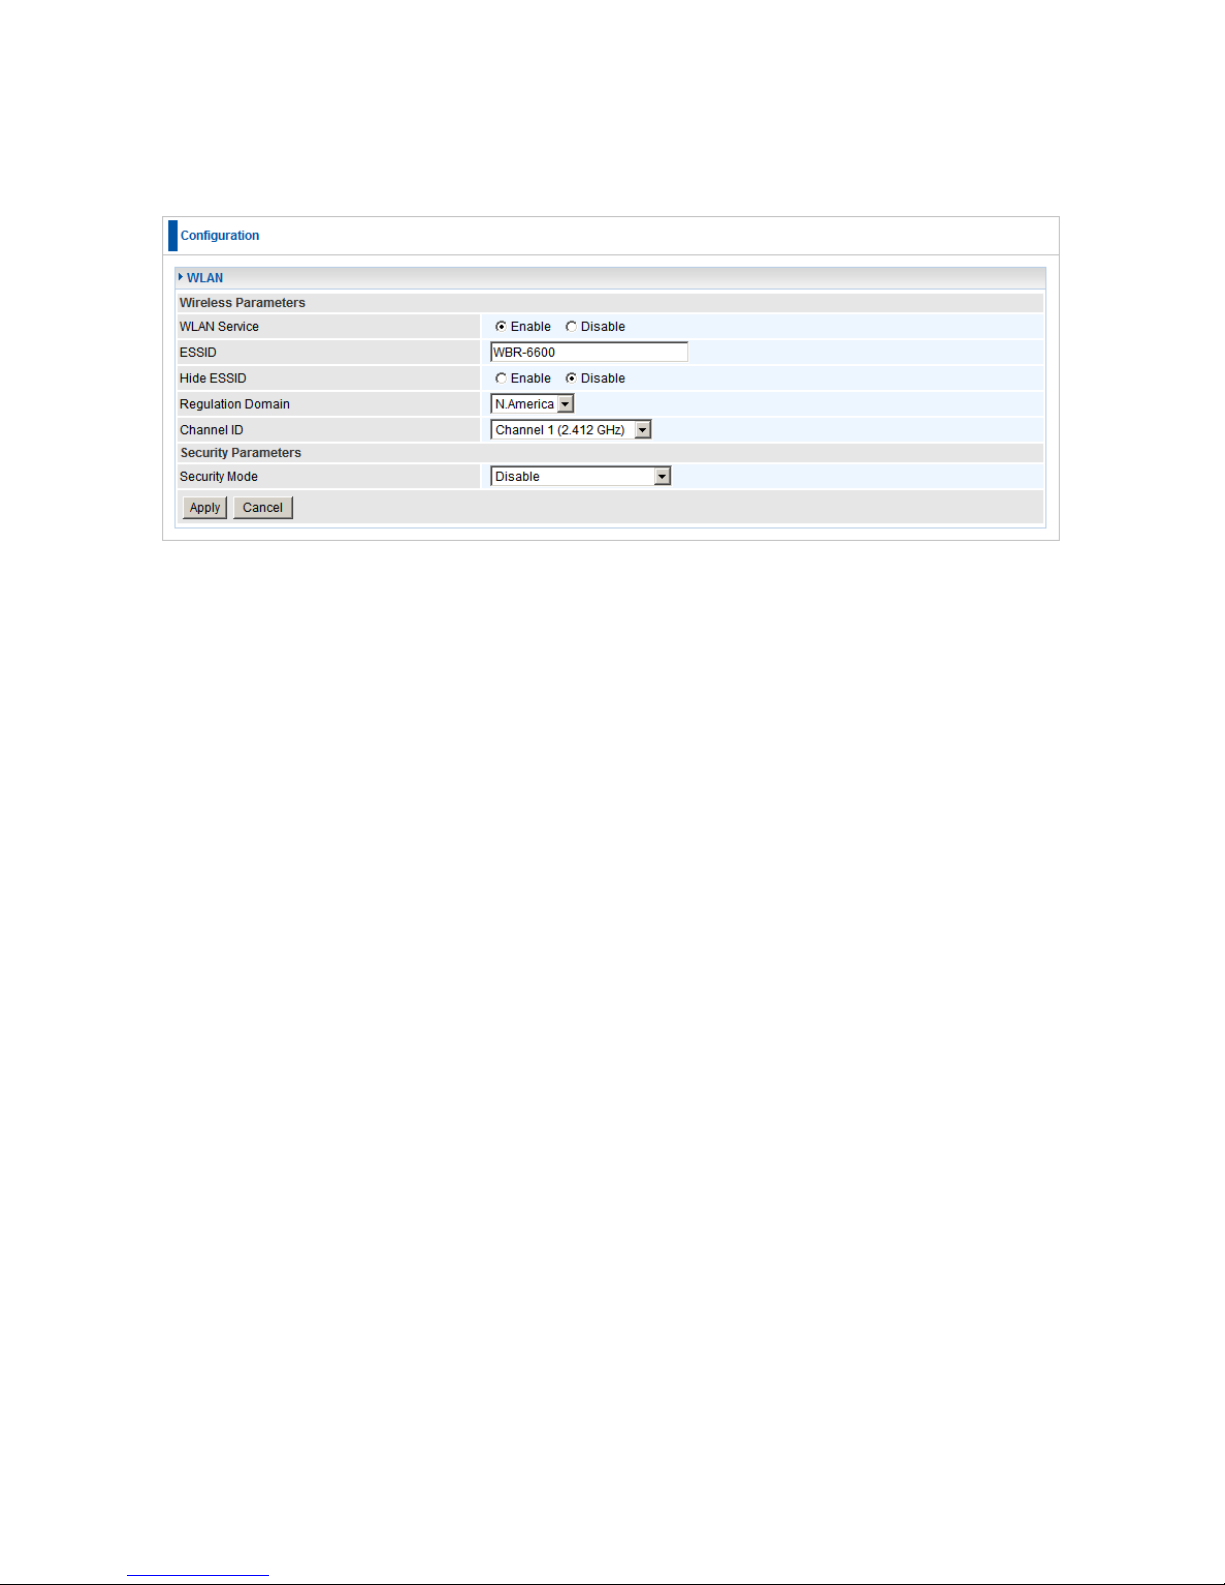
WLAN
WLAN Service: Enable or Disable Wireless function. Default setting is set to Enable.
ESSID: The ESSID is the unique name of a wireless access point (AP) to be
distinguished from another. For security propose, change to a unique ID name to the AP
which is already built-in to the router‟s wireless interface. It is case sensitive and must not
excess 32 characters. Make sure your wireless clients have exactly the ESSID as the
device, in order to get connected to your network.
Note: ESSID is case sensitive and must not excess 32 characters.
Hide ESSID: It is function in which transmits its ESSID to the air so that when wireless
client searches for a network, router can then be discovered and recognized. Default
setting is Disable.
Enable: Select Enable if you do not want broadcast your ESSID. When select
Enable, no one will be able to locate the Access Point (AP) of your router.
Disable: When Disable is selected, you can allow anybody with a wireless
client to be able to locate the Access Point (AP) of your router.
Regulation Domain: There are seven Regulation Domains for you to choose from,
including North America (N.America), Europe, France, etc. The Channel ID will be
different based on this setting.
Channel ID: Select the ID channel that you would like to use.
Security Mode: You can disable or enable with WPA or WEP for protecting wireless
network. The default mode of wireless security is Disable.
Page 36
36
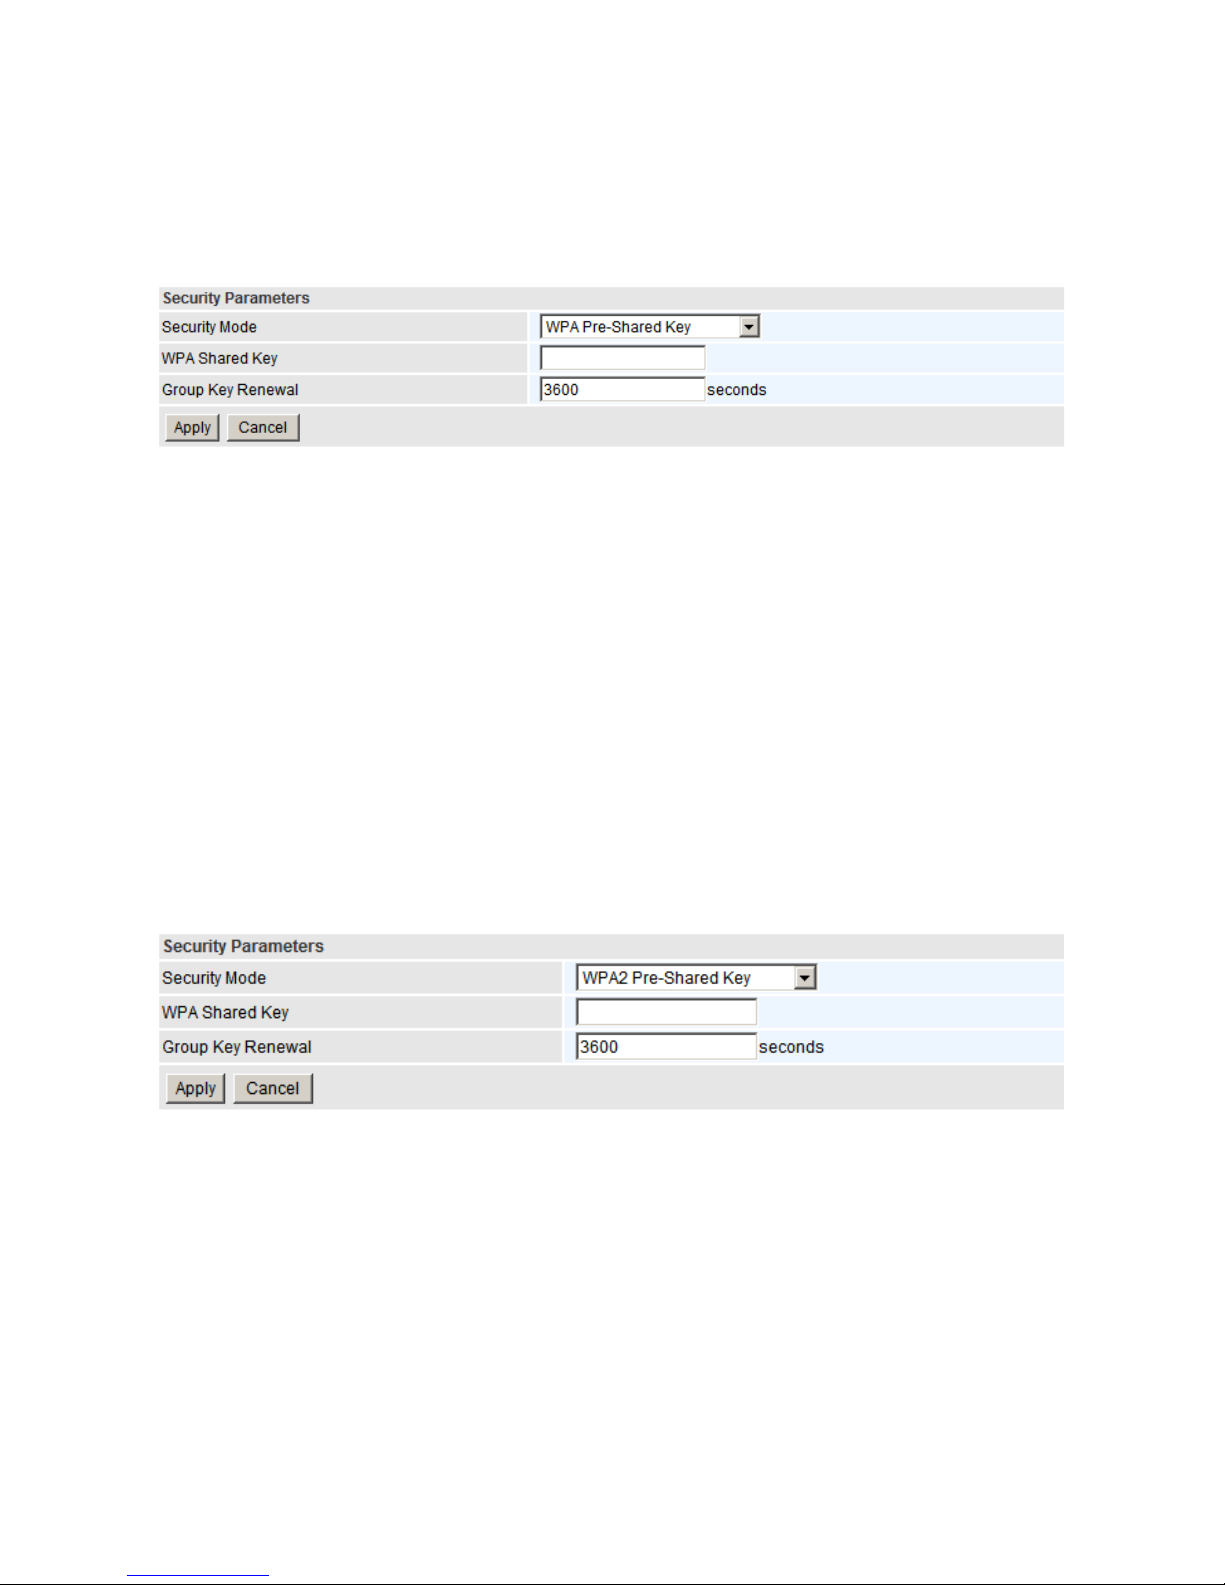
Wireless Security Parameters
WPA Pre-Shared Key
WPA Shared Key: The key for network authentication. The input format is in character
style and the key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
between wireless client and Access Point (AP). This process is done automatically.
Note: In basic mode, WPA will utilize TKIP encryption method. If you want to use WPA
with AES encryption, please go to Advanced settings.
WPA2 Pre-Shared Key
WPA2 Shared Key: The key for network authentication. The input format is in
character style and key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
between wireless client and Access Point (AP). This process is done automatically.
Note: In basic mode, WPA2 will utilize AES encryption method. If you want to use WPA2
with TKIP encryption, please go to Advanced settings.
Page 37
37
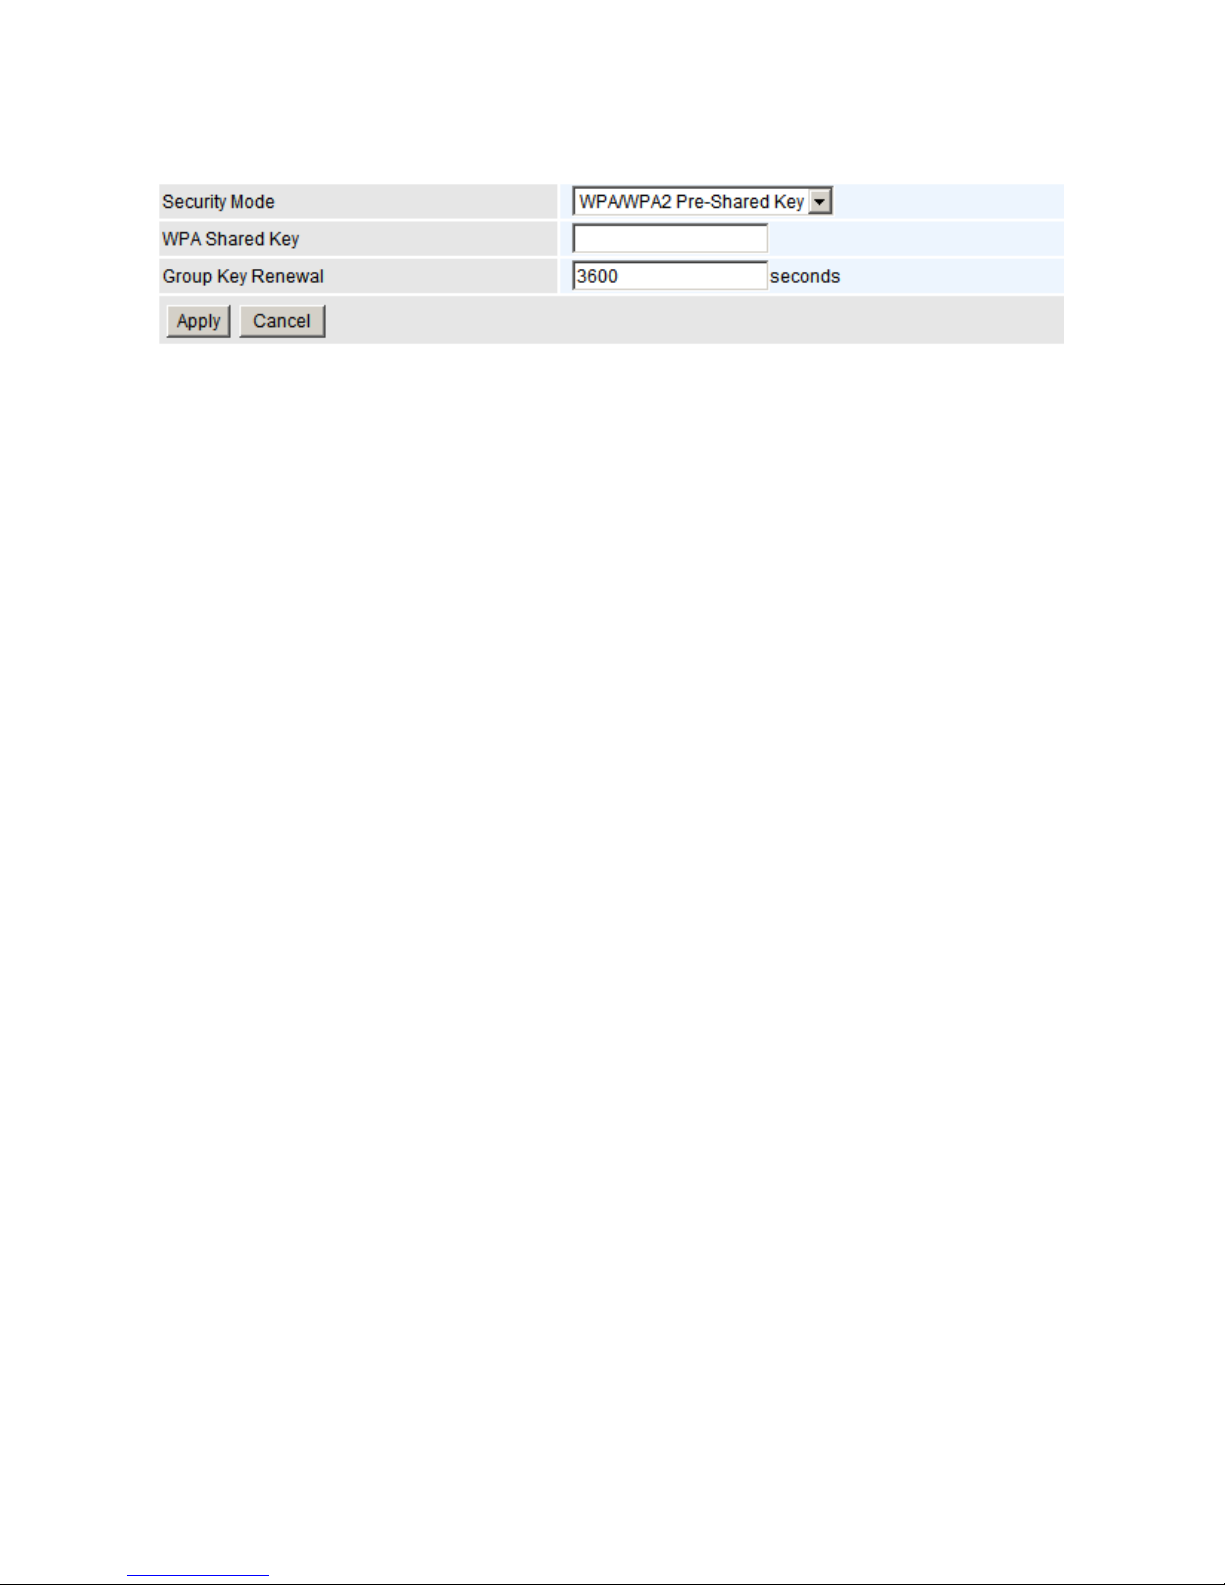
WPA/WPA2 Pre-Shared Key
In this mode, the router will accept both WPA and WPA2 wireless clients
WPA Shared Key: The key for network authentication. The input format is in character
style and key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
between wireless client and Access Point (AP). This process is done automatically.
Page 38
38
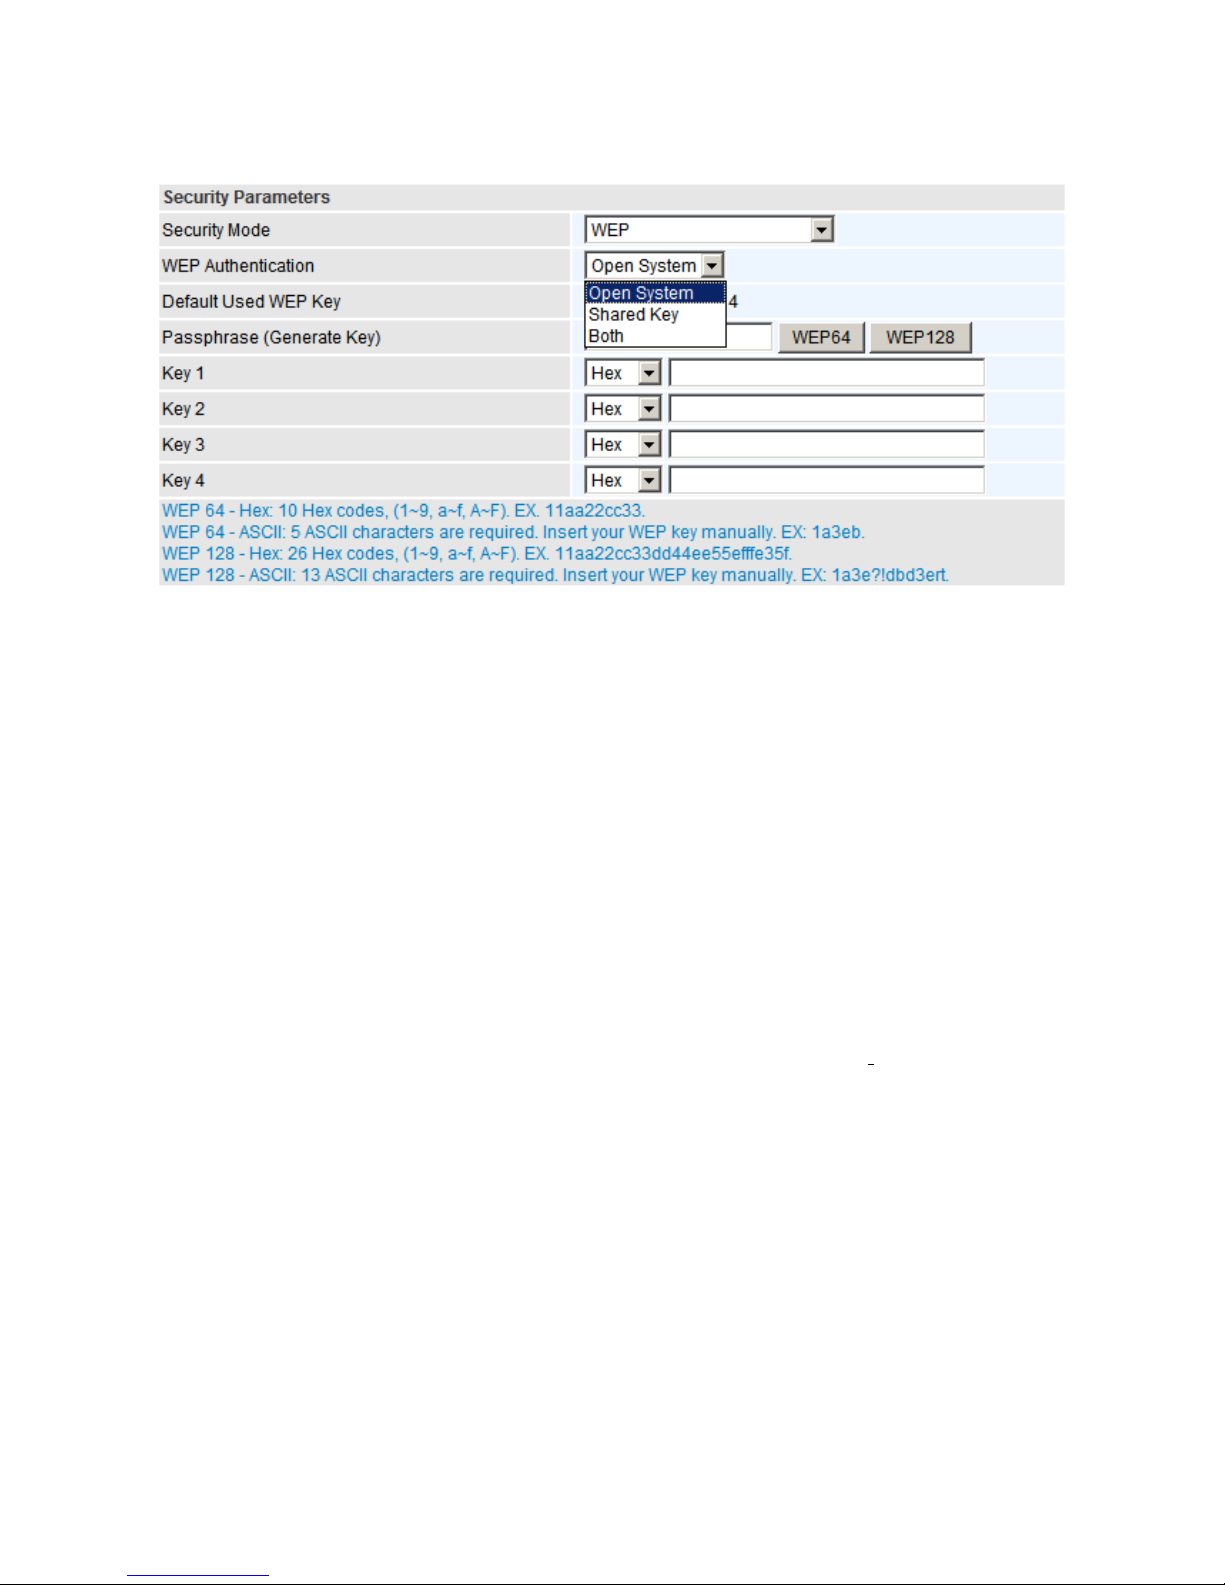
WEP
WEP Authentication: To prevent unauthorized wireless stations from accessing data
transmitted over the network, the router offers secure data encryption, known as WEP.
If you require high security for transmissions, there are three options to select from:
Open System, Share key or Both.
Default Used WEP Key: Select the encryption key ID; please refer to Key (1~4) below.
Passphrase: This is used to generate WEP keys automatically based upon the input
string and a pre-defined algorithm in WEP64 or WEP128. You can input the same
string in both the AP and Client card settings to generate the same WEP keys. Please
note that you do not have to enter Key (1-4) as below when the Passphrase is
enabled.
Key (1-4): Enter the key to encrypt wireless data. To allow encrypted data transmission,
the WEP Encryption Key values on all wireless stations must be the same as the router.
There are four keys for your selection. The input format is in HEX or ASCII style, 5 and
13 ASCII codes are required for WEP64 and WEP128 respectively no any separator is
included.
Page 39
39
Chapter 5 – Advance Configuration
Once you have logged on to your WBR-6600 Router via your web browser, you can begin to
set it up according to your requirements. On the configuration homepage, the left navigation
pane links you directly to the setup pages, which include:
Basic (Switch to Basic Configuration Mode)
Status (ADSL Status, ARP Table, DHCP Table, System Log, Firewall Log, UPnP
Portmap)
Quick Start
Configuration (LAN, WAN, System, Firewall, QoS, Virtual Server, Wake on LAN, Time
Schedule and Advanced)
The following sections provide an overview of the settings available for configuring your
router.
Page 40
40
Status Page
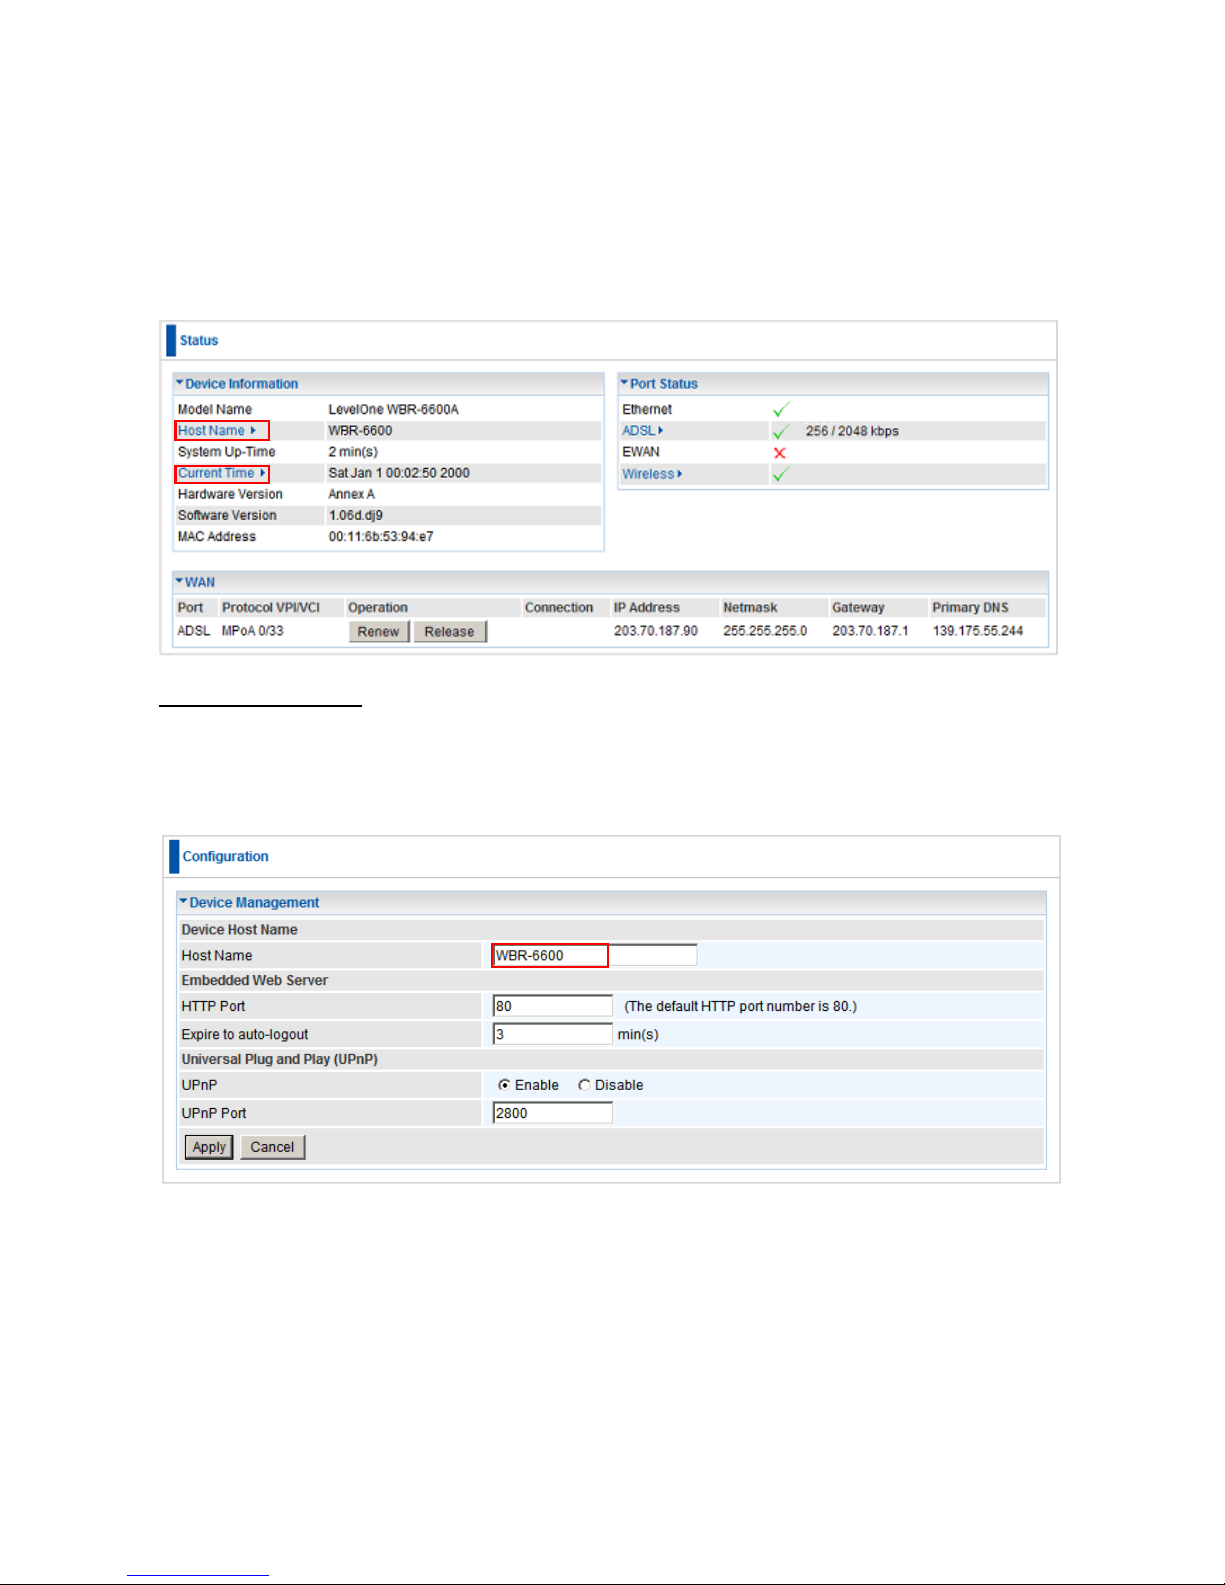
This page shows you the current status of the WBR-6600, with advanced options such as
Host Name and Time settings.
Device Information
Model Name: The model name of the device.
Host Name: Provide a name for the router for identification purposes. Host Name lets
you change the router name. Click on Host Name to direct you to the following page:
System Up-Time: Records system up-time.
Current time: Set the current time. See the Time Zone section for more information.
Hardware Version: Device version.
Software Version: Firmware version.
MAC Address: The LAN MAC address.
Page 41
41
Port Status
Port Status: User can look up to see if they are connected to Ethernet, ADSL, EWAN or
Wireless.
WAN
Port: Name of the WAN connection.
Protocol VPI/VCI: Virtual Path Identifier and Virtual Channel Identifier
Operation: Current available operation.
Connection: The current connection status.
IP Address: WAN port IP address.
Netmask: WAN port IP subnet mask.
Gateway: The IP address of the default gateway.
Primary DNS: The IP address of the primary DNS server.
Port Status: User can look up to see if they are connected to Ethernet, ADSL.
Page 42
42
ADSL Status
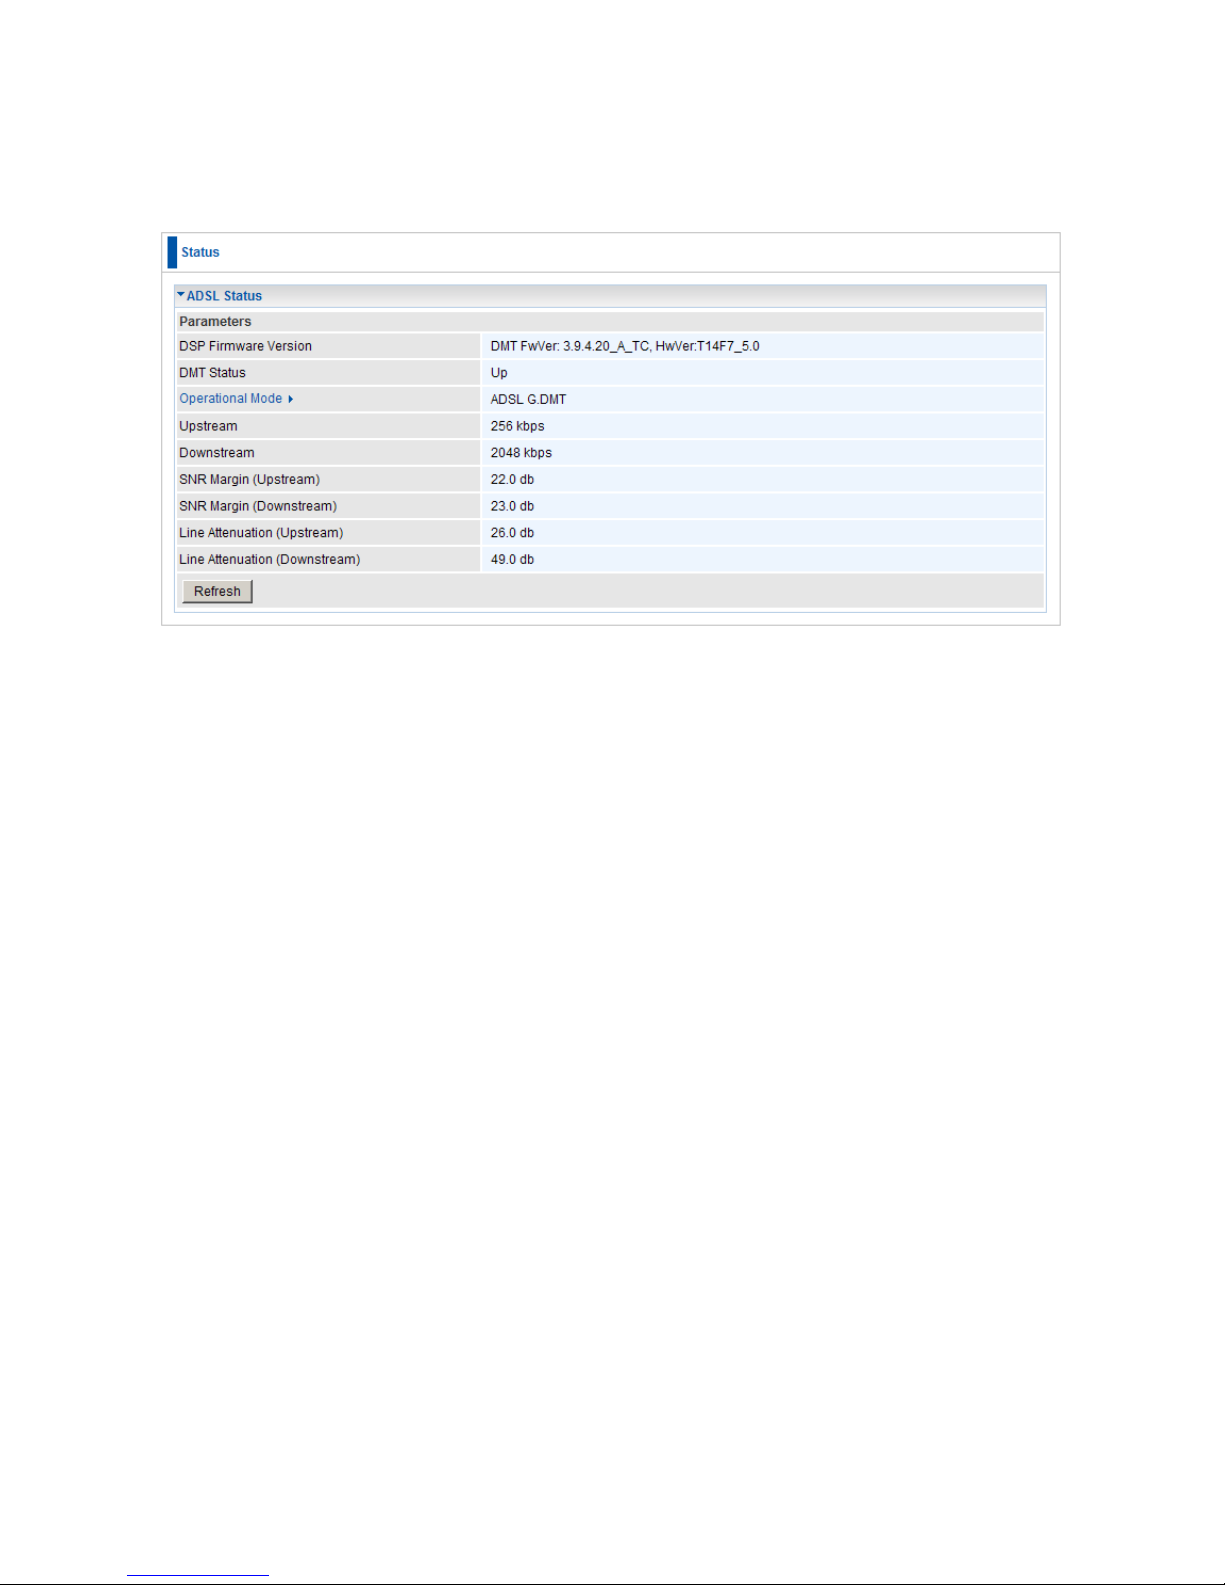
This page shows you the current status of the WBR-6600‟s ADSL connection.
DSP Firmware Version: DSP code version
DMT Status: Current DMT Status
Operational Mode: To show the state when user select “AUTO” on connect mode.
Upstream: Upstream rate.
Downstream: Downstream rate.
SNR Margin (Upstream): This is noise margin in upstream.
SNR Margin (Downstream): This is noise margin in downstream.
Line Attenuation (Upstream): This is attenuation of signal in upstream.
Line Attenuation (Downstream): This is attenuation of signal in downstream.
Page 43
43
Operational Mode
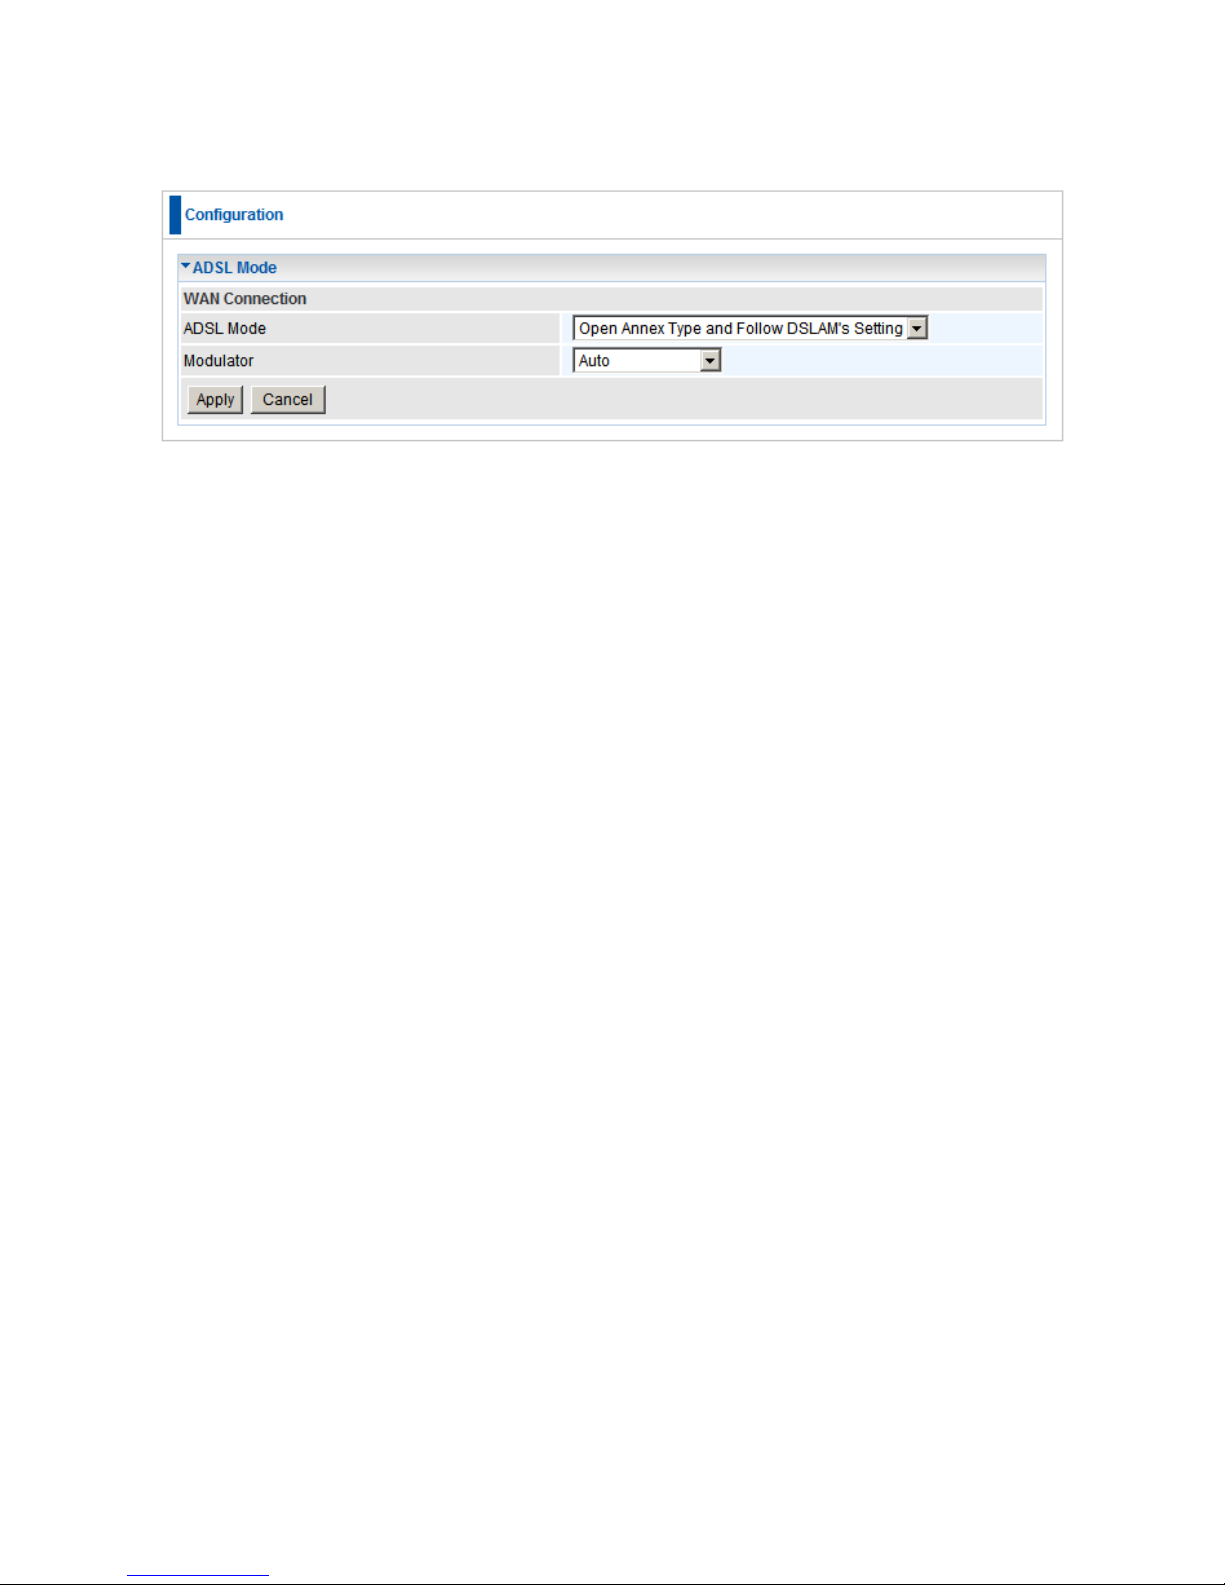
ADSL Mode: There are four modes “Open Annex Type and Follow DSLAM’s
Setting”, ”Annex A”, ”Annex L”, ”Annex M” and “Annex J” that user can select for this
connection.
Modulator: There are seven modes “AUTO”,”ADSL
Multimode”,”ADSL2”, ”ADSL2+”,”G.Lite”, “T1.413” and “G.DMT” that user can select for
this connection.
Page 44
44
ARP Table
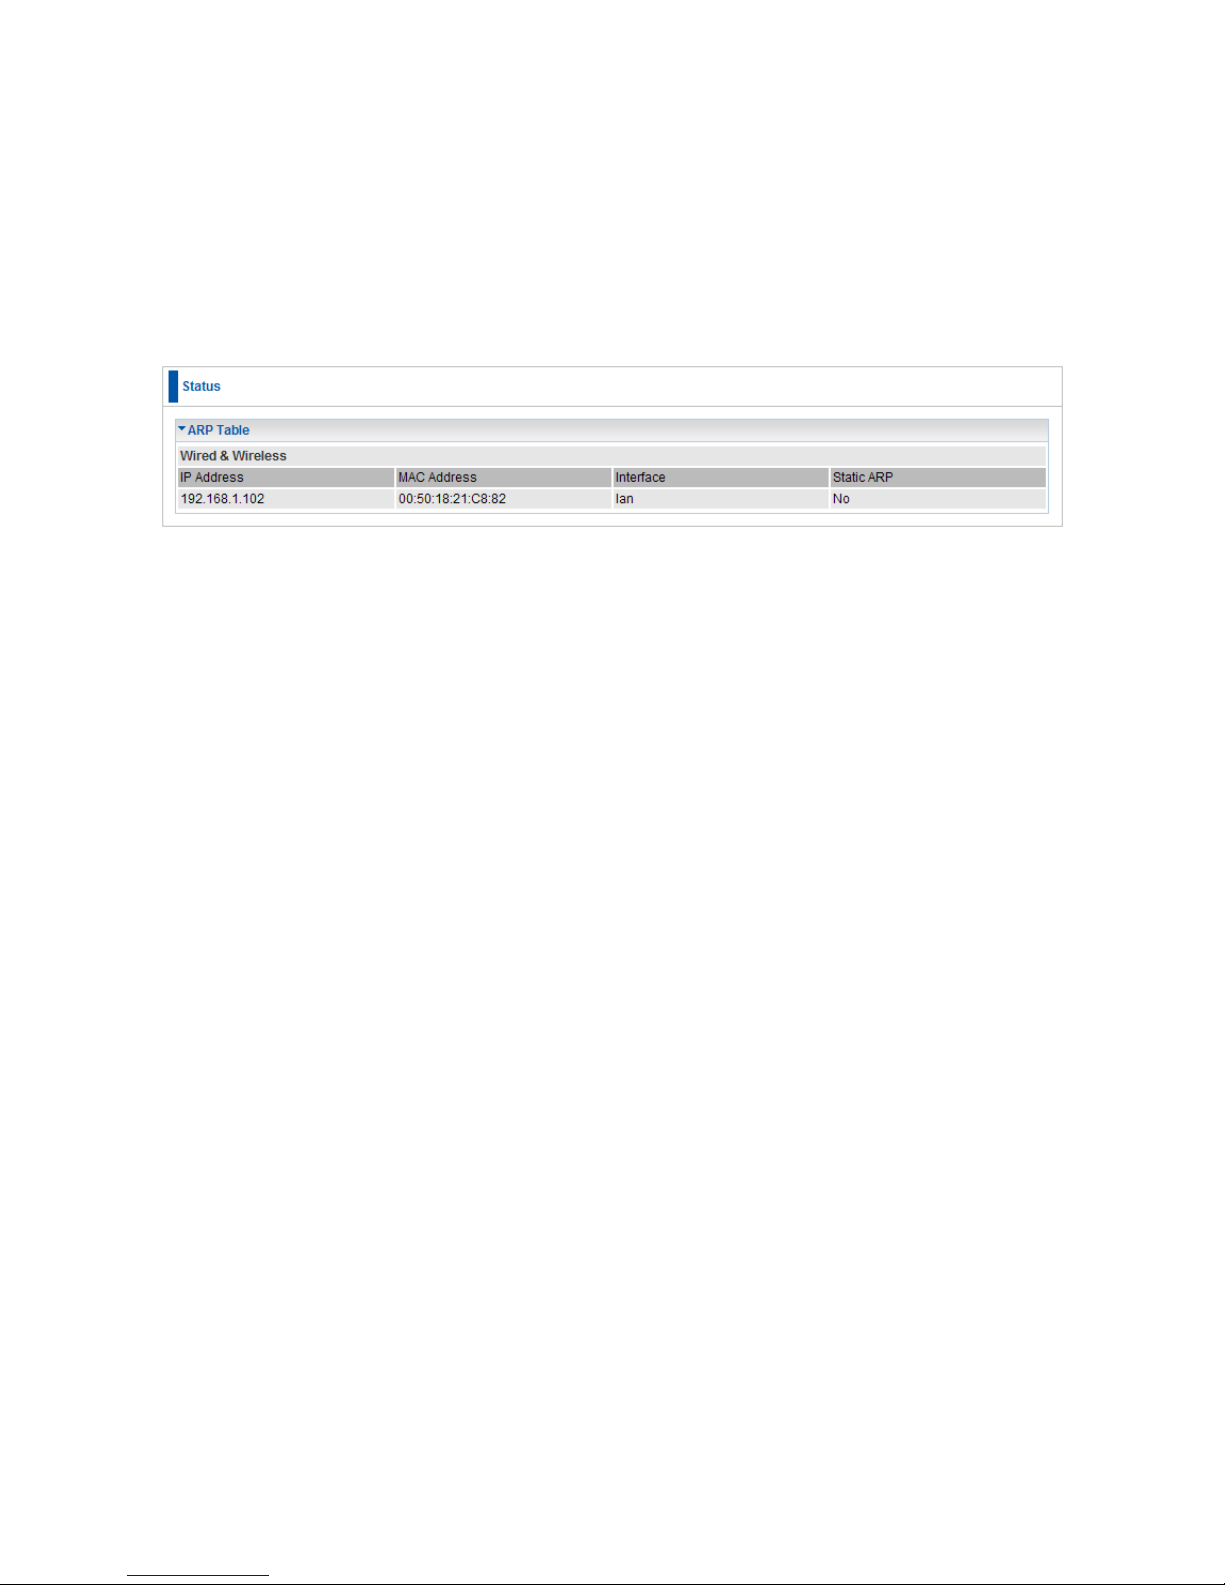
This section displays the router‟s ARP (Address Resolution Protocol) Table, which shows
the mapping of Internet (IP) addresses to Ethernet (MAC) addresses. This is useful as a
quick way of determining the MAC address of the network interface of your PCs to use
with the router‟s Firewall – MAC Address Filter function. See the Firewall section of this
manual for more information on this feature.
IP Address: It is IP Address of internal host that join this network.
MAC Address: The MAC address of internal host.
Page 45
45
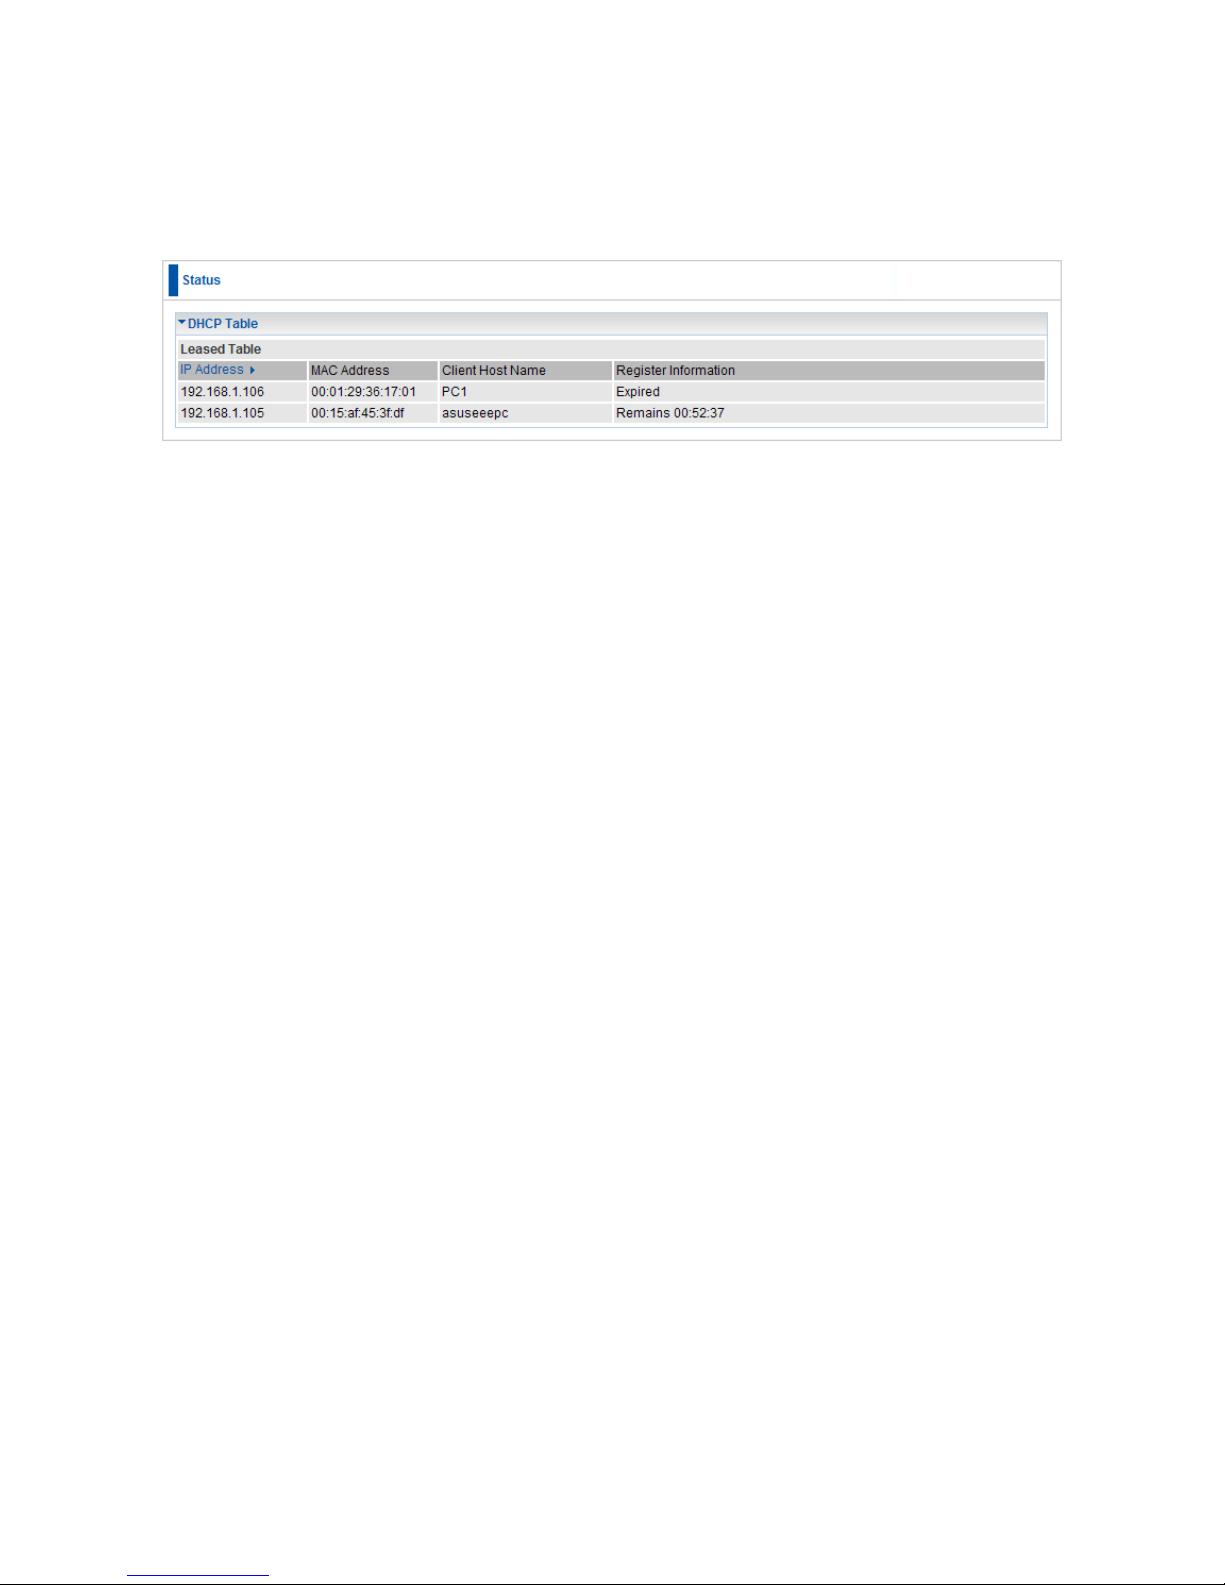
DHCP Table
This page shows you the network clients (Notebooks or PCs) that are allocated IP
Addresses by the WBR-6600‟s DHCP Server.
IP Address: The current corresponding DHCP-assigned dynamic IP address of the
device.
MAC Address: The MAC Address of internal DHCP client host.
Client Host Name: The Host Name of internal DHCP client.
Register Information: Register time information
Page 46
46
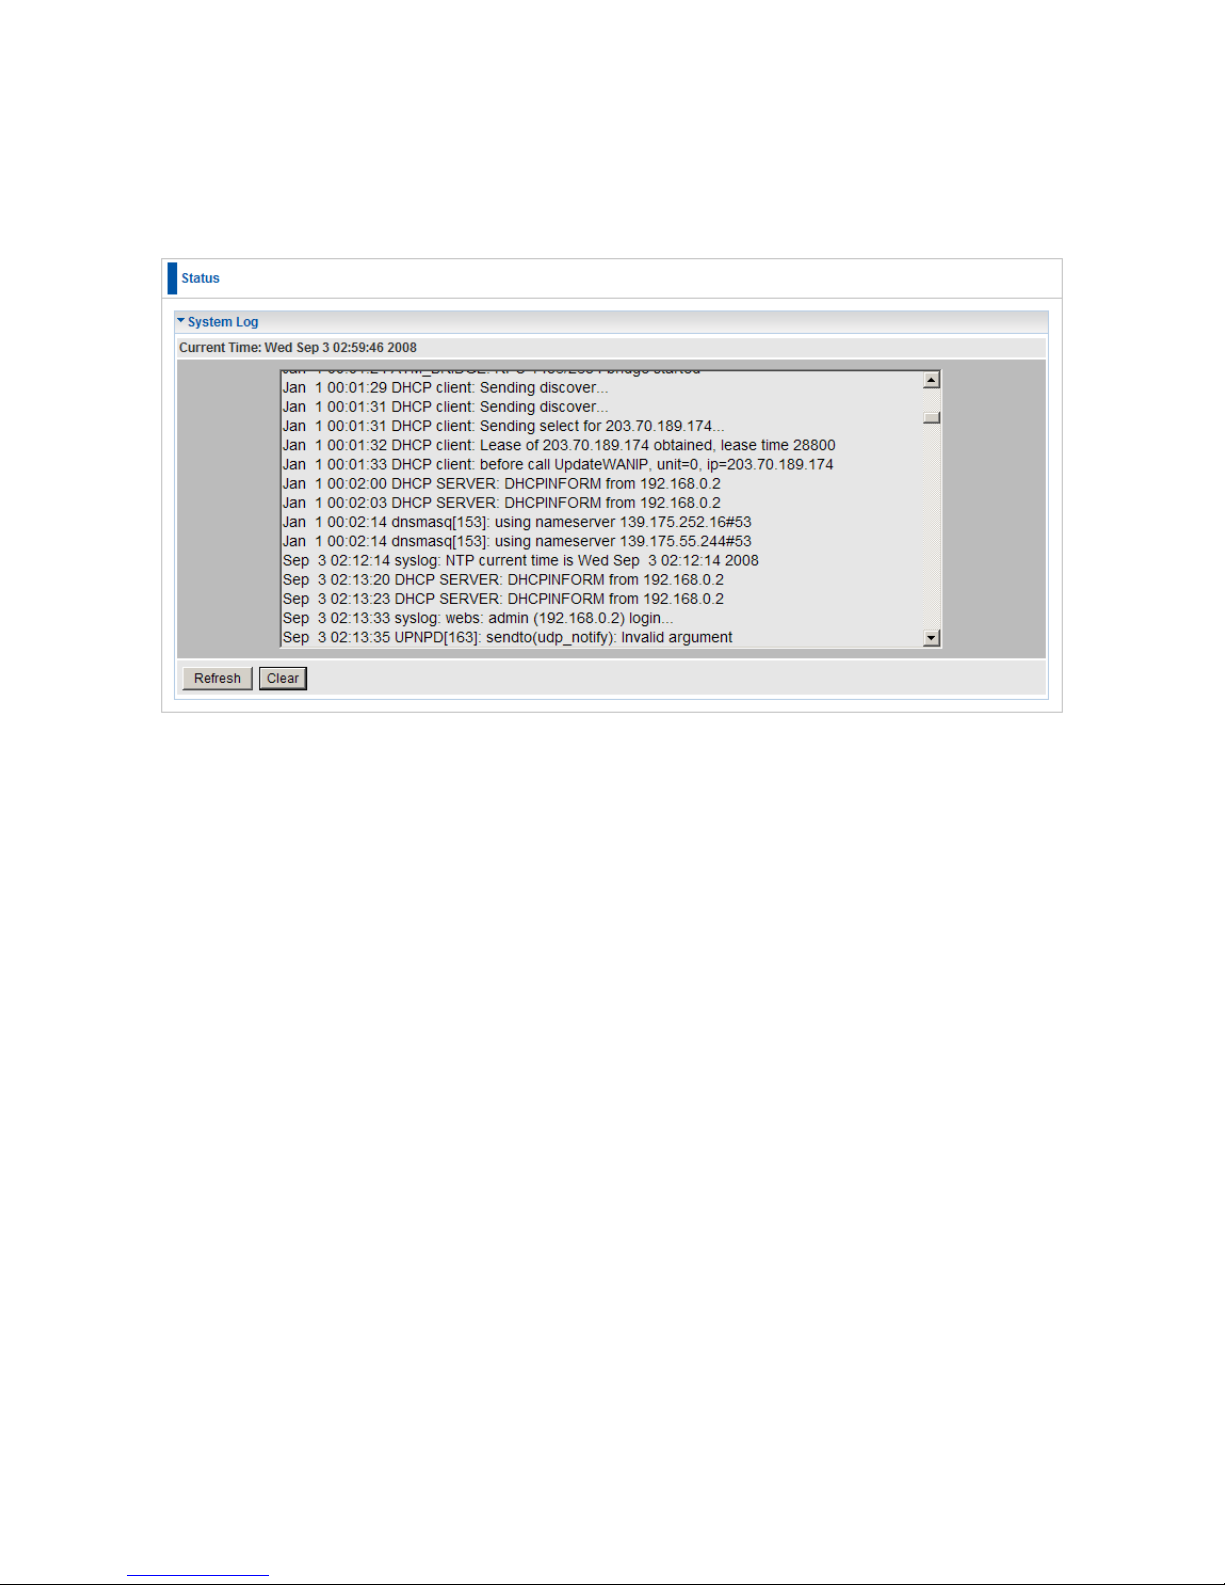
System Log
Display system logs accumulated up to the present time. You can trace historical
information with this function.
Page 47
47
Firewall Log
Firewall Log displays log information of any unexpected action with your firewall settings.
This page displays the router‟s Firewall Log entries. The log shows log entries when you
have enabled Intrusion Detection or Block WAN PING in the Configuration – Firewall
section of the interface. Please see the Firewall section of this manual for more details
on how to enable Firewall logging.
Page 48
48
UPnP Portmap
The section lists all port-mapping established using UPnP (Universal Plug and Play).
Please see the Advanced section of this manual for more details on UPnP and the
router‟s UPnP configuration options.
Page 49
49
Quick Start
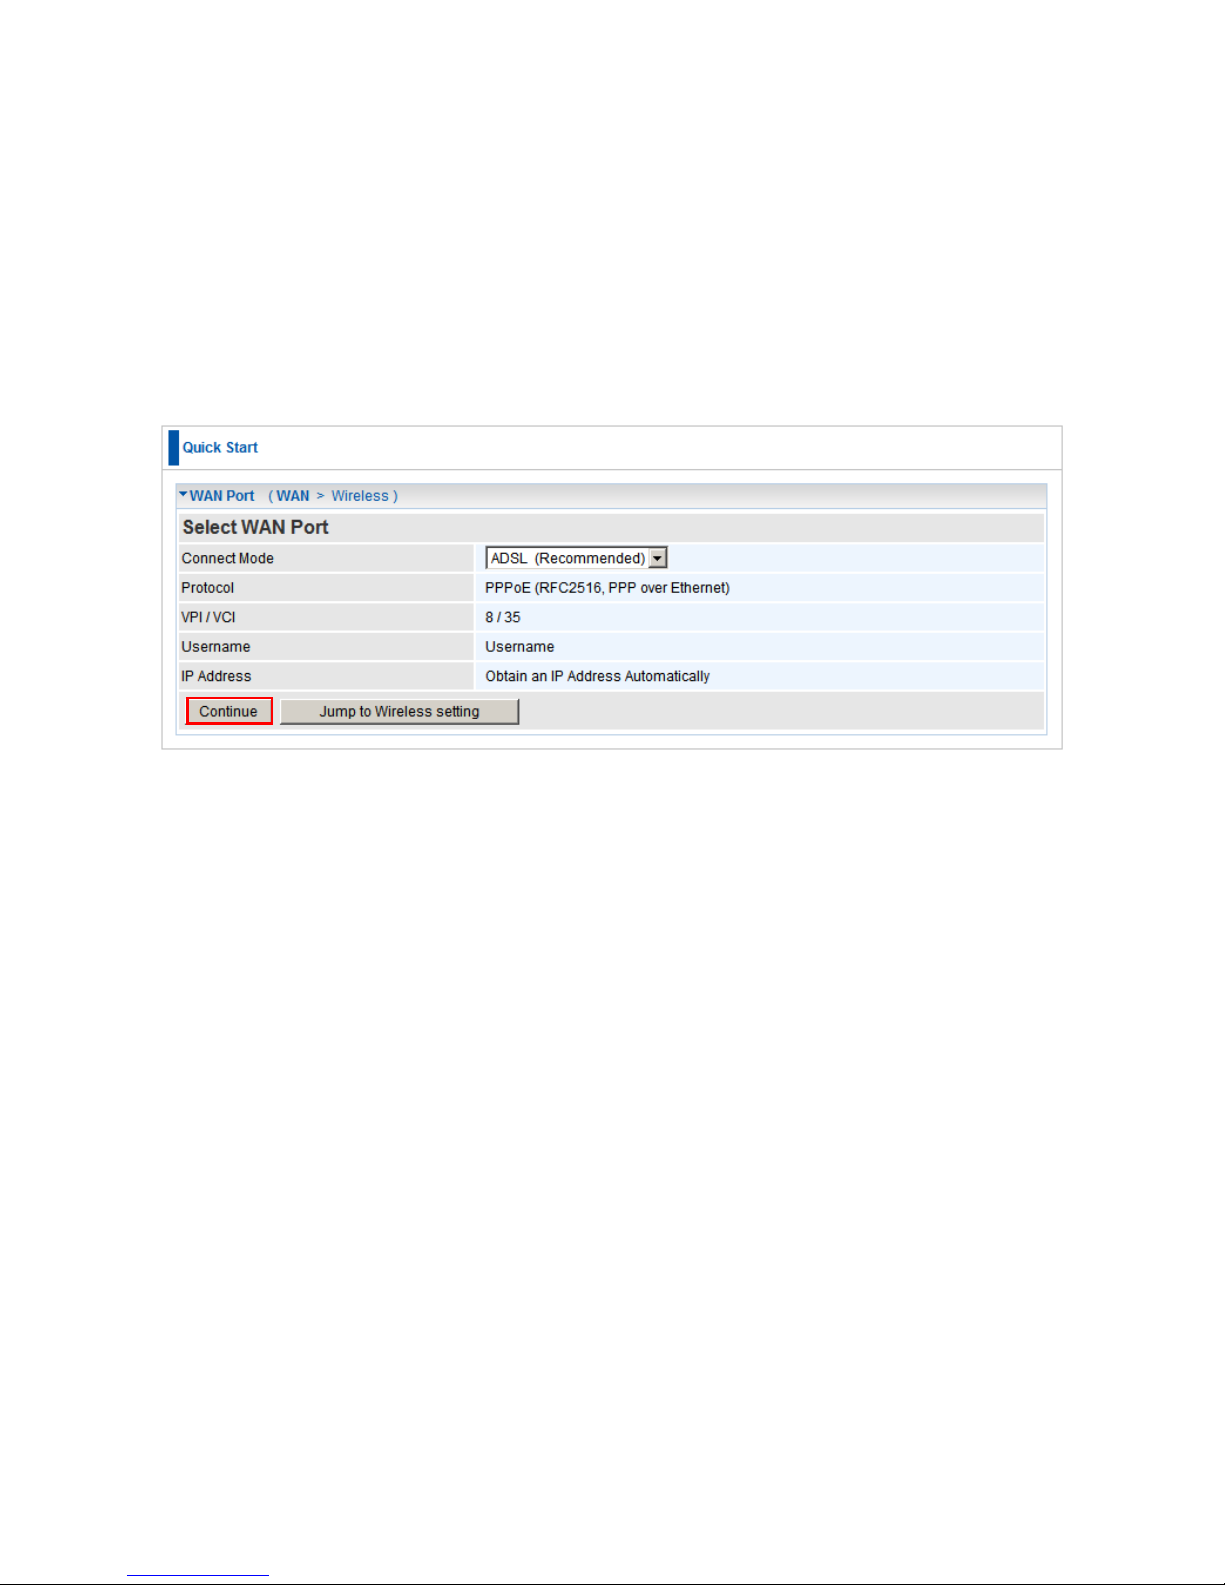
This wizard is similar to Easy Sign On, and will guide you through setting up your
WBR-6600.
Click ”Continue” to start the wizard. The steps are the same as the Easy Sign On.
ADSL
Connect mode: ADSL
Protocol: The current ATM protocol in the device
VPI / VCI: The current value of VPI / VCI in the device
IP address: To show current value of IP address in the device.
Page 50
50
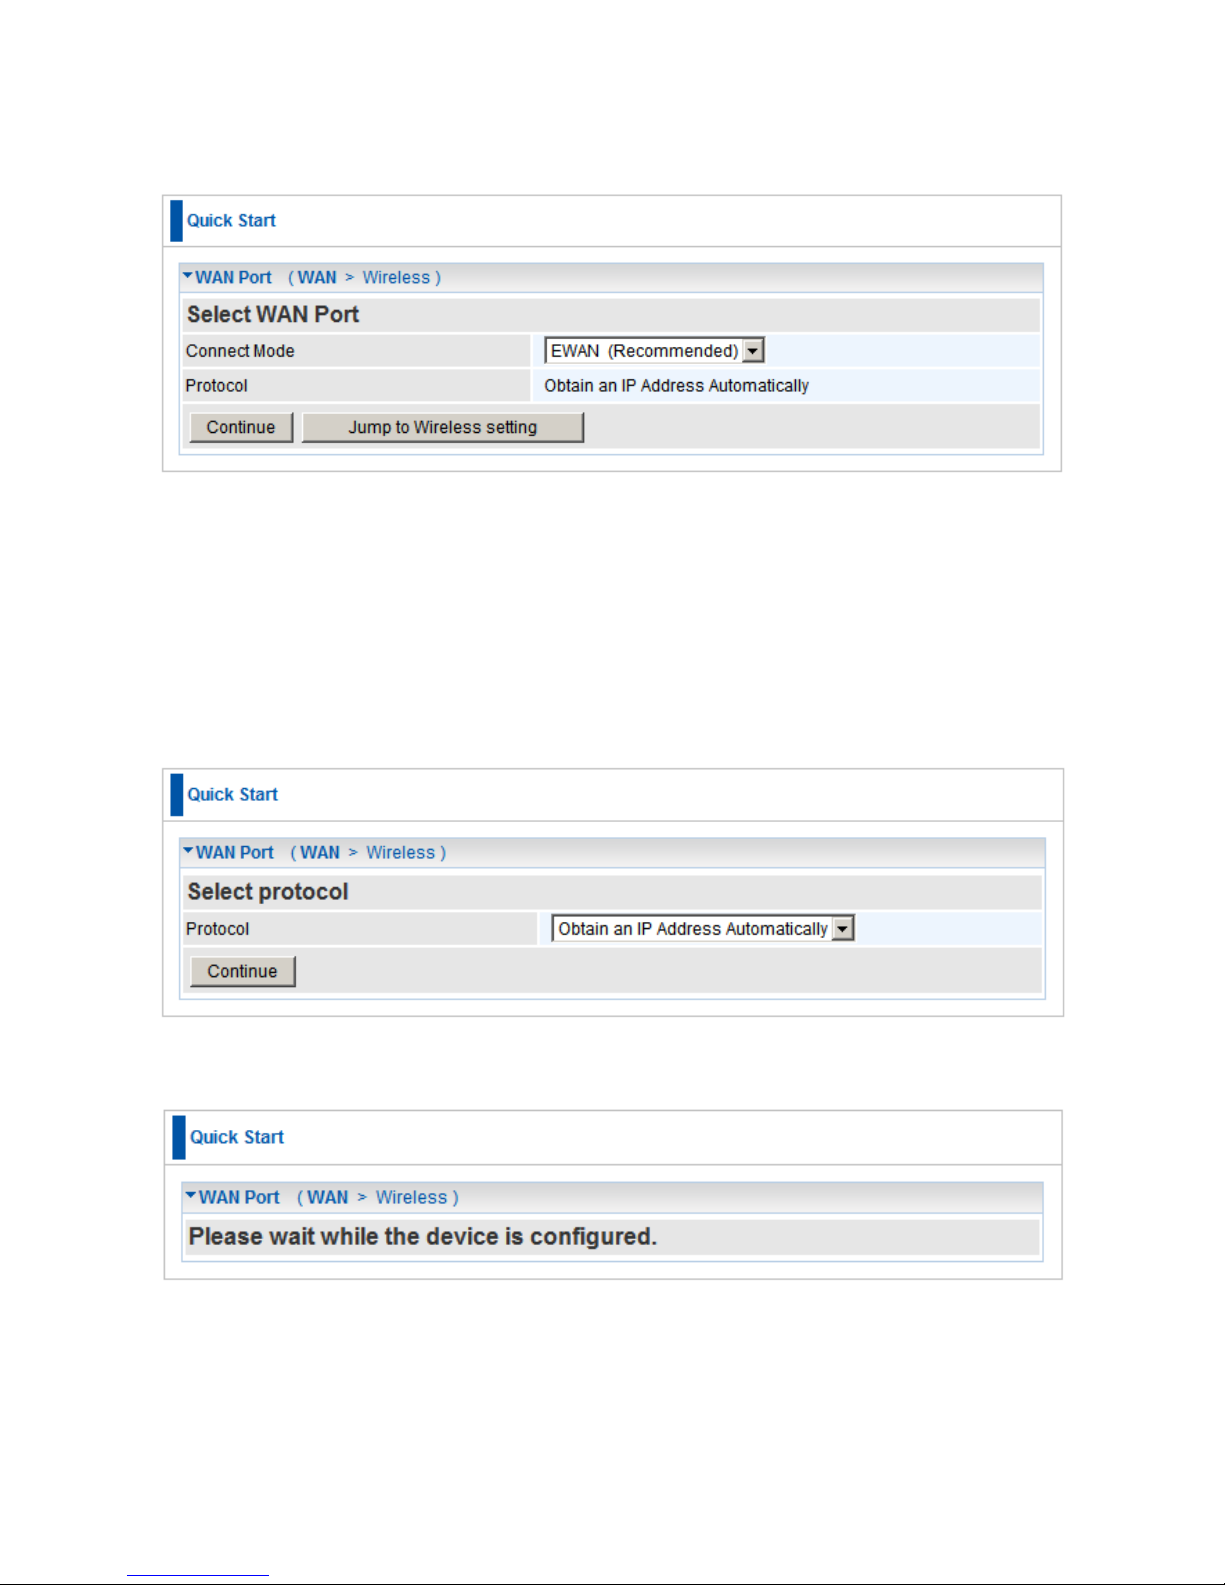
EWAN
Click on Continue to choose the Protocol to connect with EWAN or click Jump to
Wireless Setting to use Protocol: Obtain an IP Address Automatically to connect and
setup wireless settings at the same time.
Obtain an IP Address Automatically
When connecting to the ISP, the WBR-6600 also functions as a DHCP client. WBR-6600
can automatically obtain an IP address, subnet mask, gateway address, and DNS server
addresses if the ISP assigns this information via DHCP.
Click on the Continue button and wait for your connection to be connected.
Page 51
51
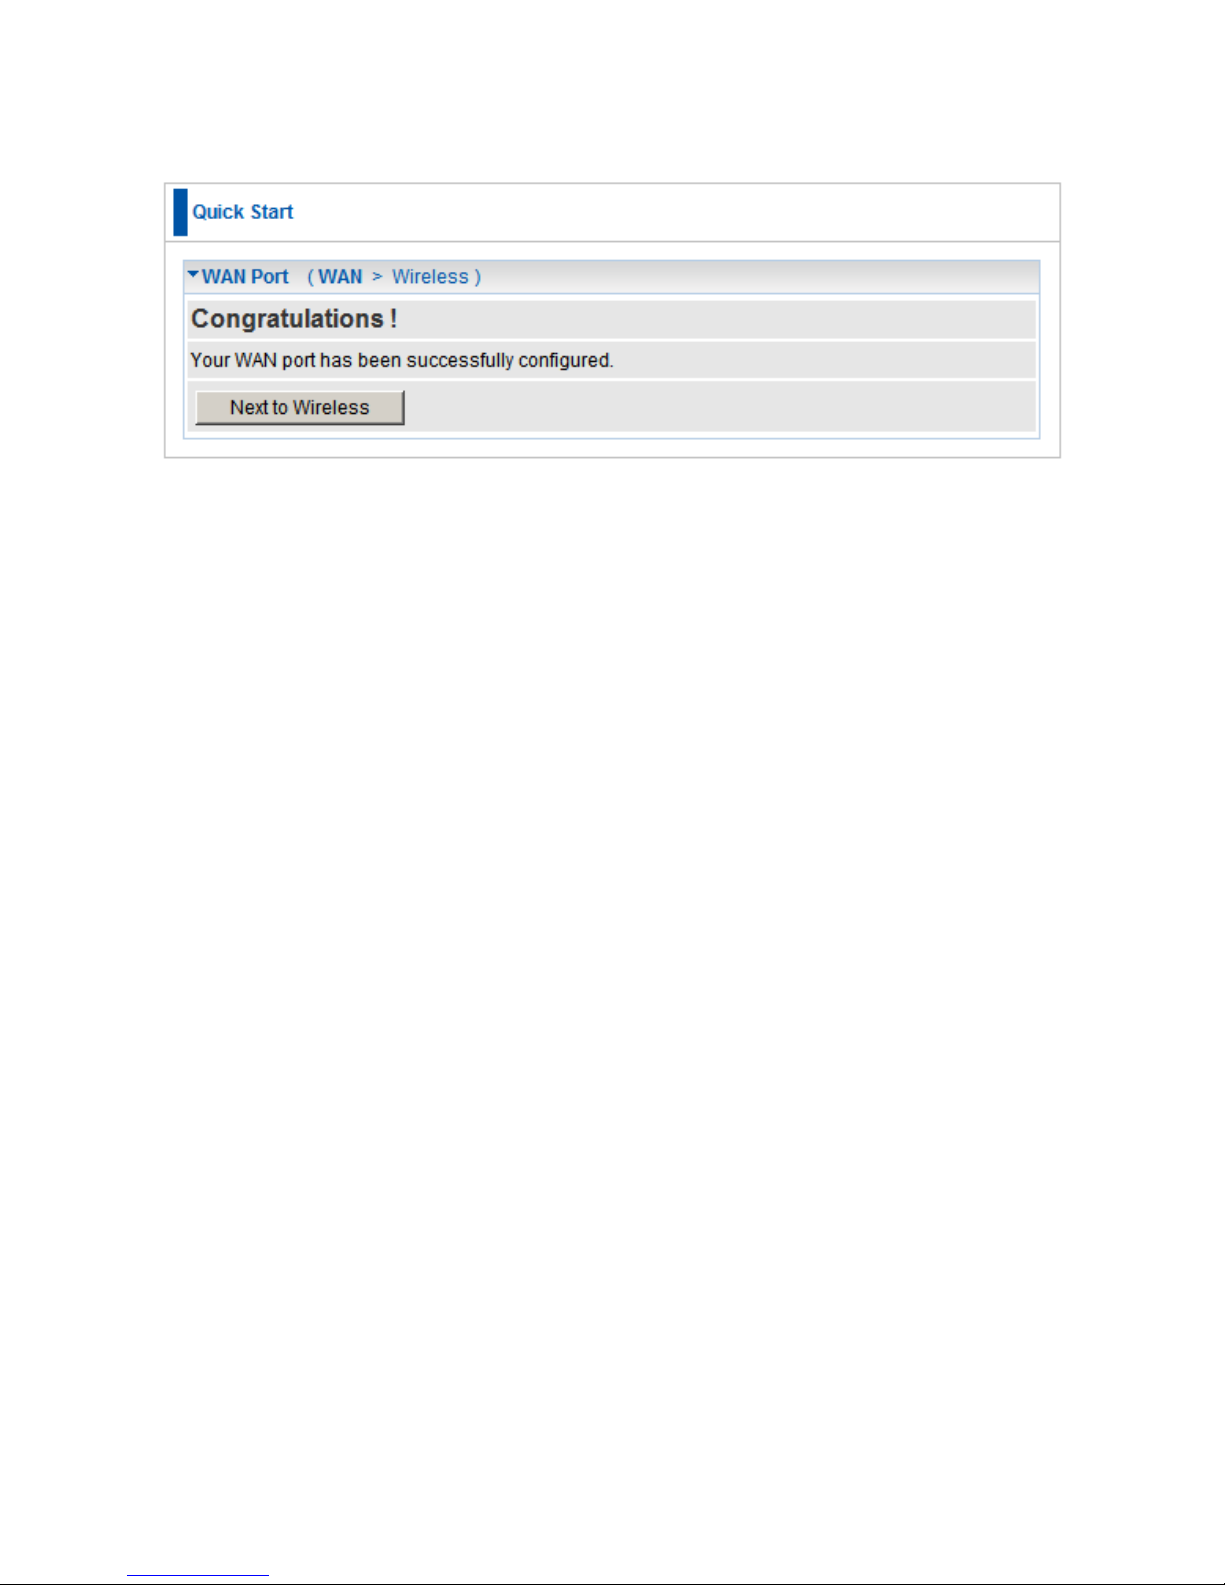
If connection is successful the following image will be shown.
Page 52
52
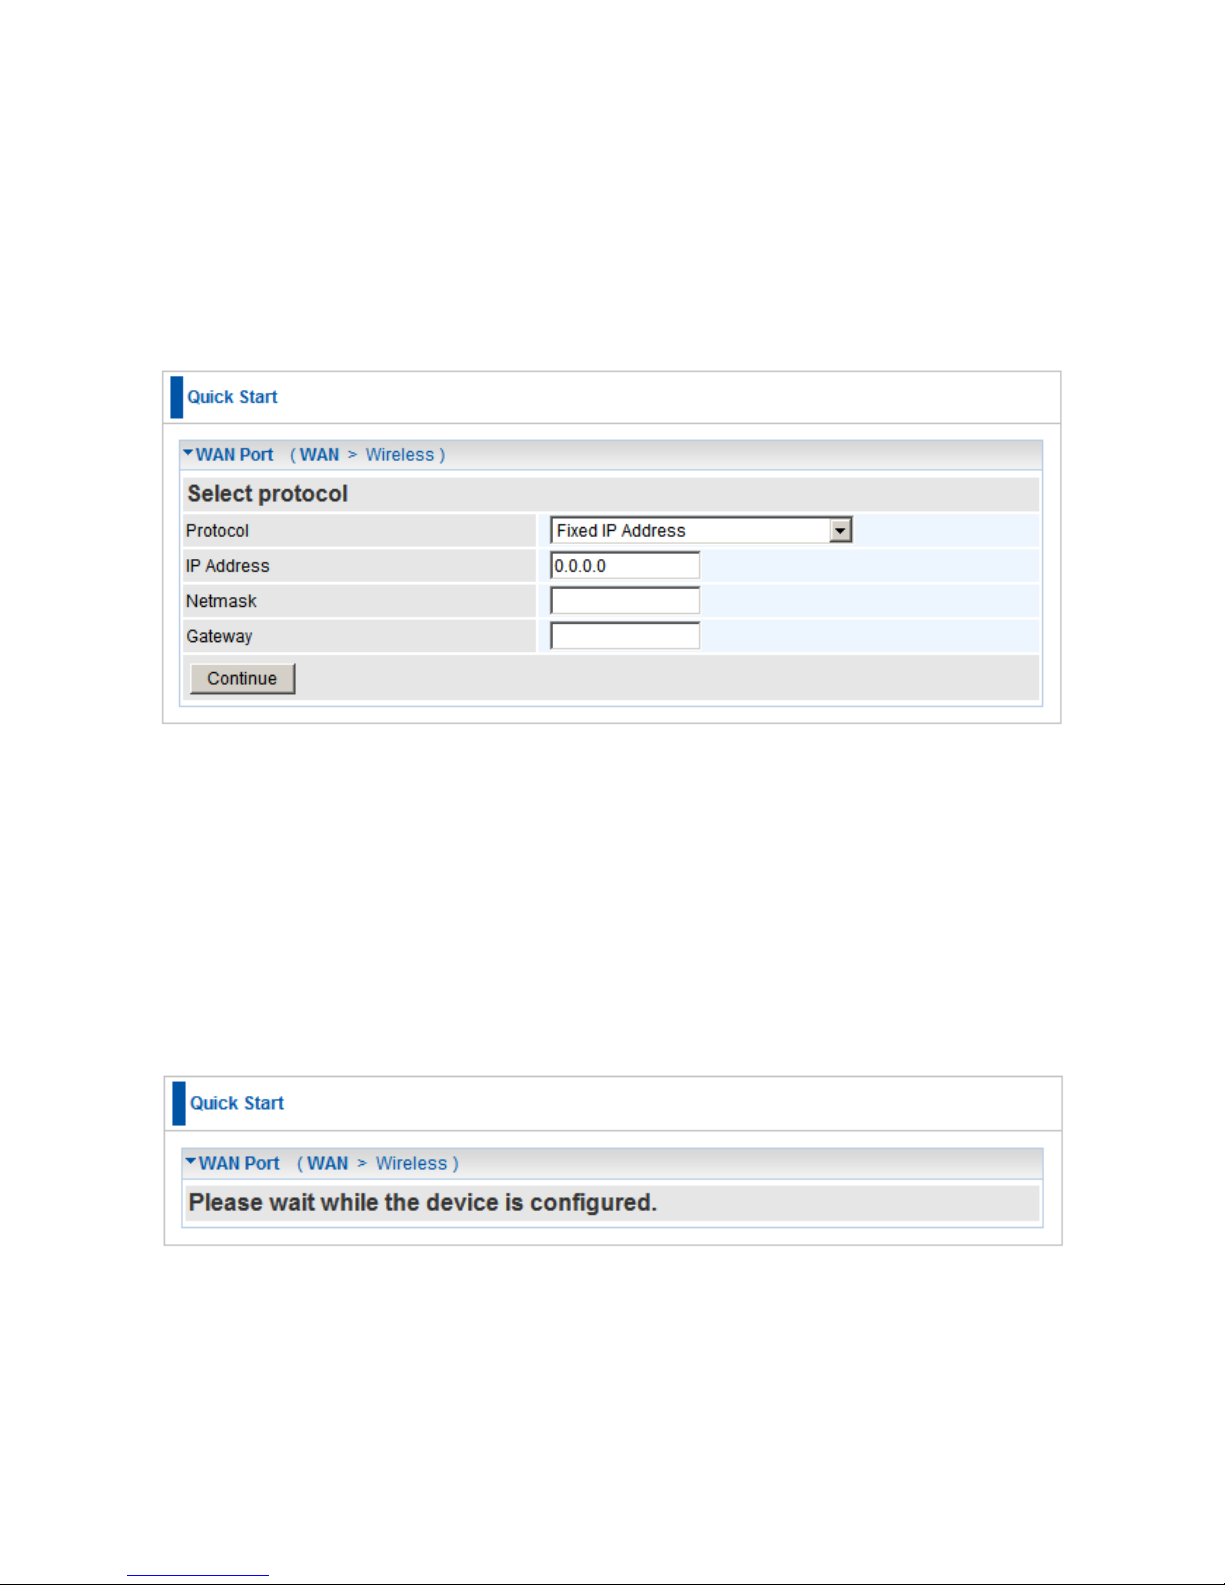
Fixed IP Address
Select this option to set static IP information. You will need to enter in the Connection
type, IP address, Netmask, and gateway address, provided to you by your ISP. Each IP
address entered in the fields must be in the appropriate IP form, which is four IP octets
separated by a dot (x.x.x.x). The Router will not accept the IP address if it is not in this
format.
Protocol: The current ATM protocol in the device
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Netmask: The default is 0.0.0.0. User can change it to other such as
255.255.255.0.Type the subnet mask assigned to you by your ISP (if given).
Gateway: You must specify a gateway IP address (supplied by your ISP)
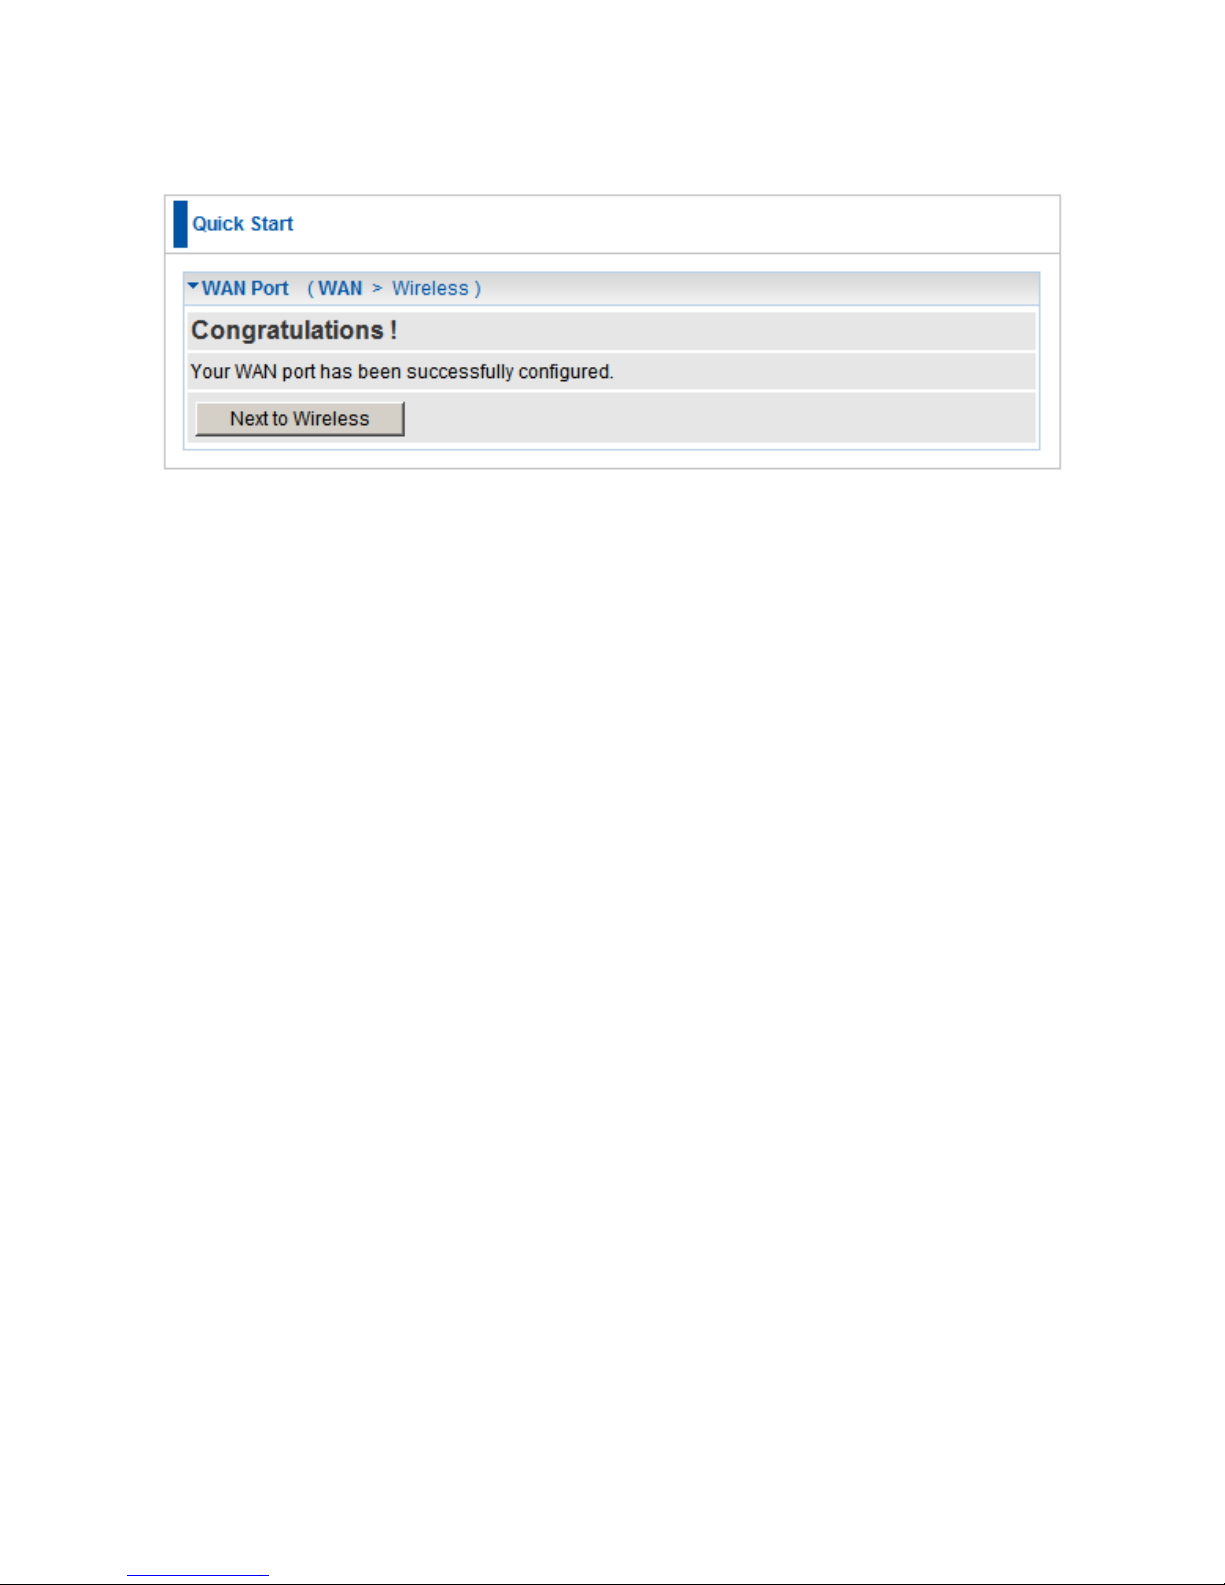
Click on the Continue button and wait for your connection to be connected.
Page 53
53
If connection is successful the following image will be shown.
Page 54
54
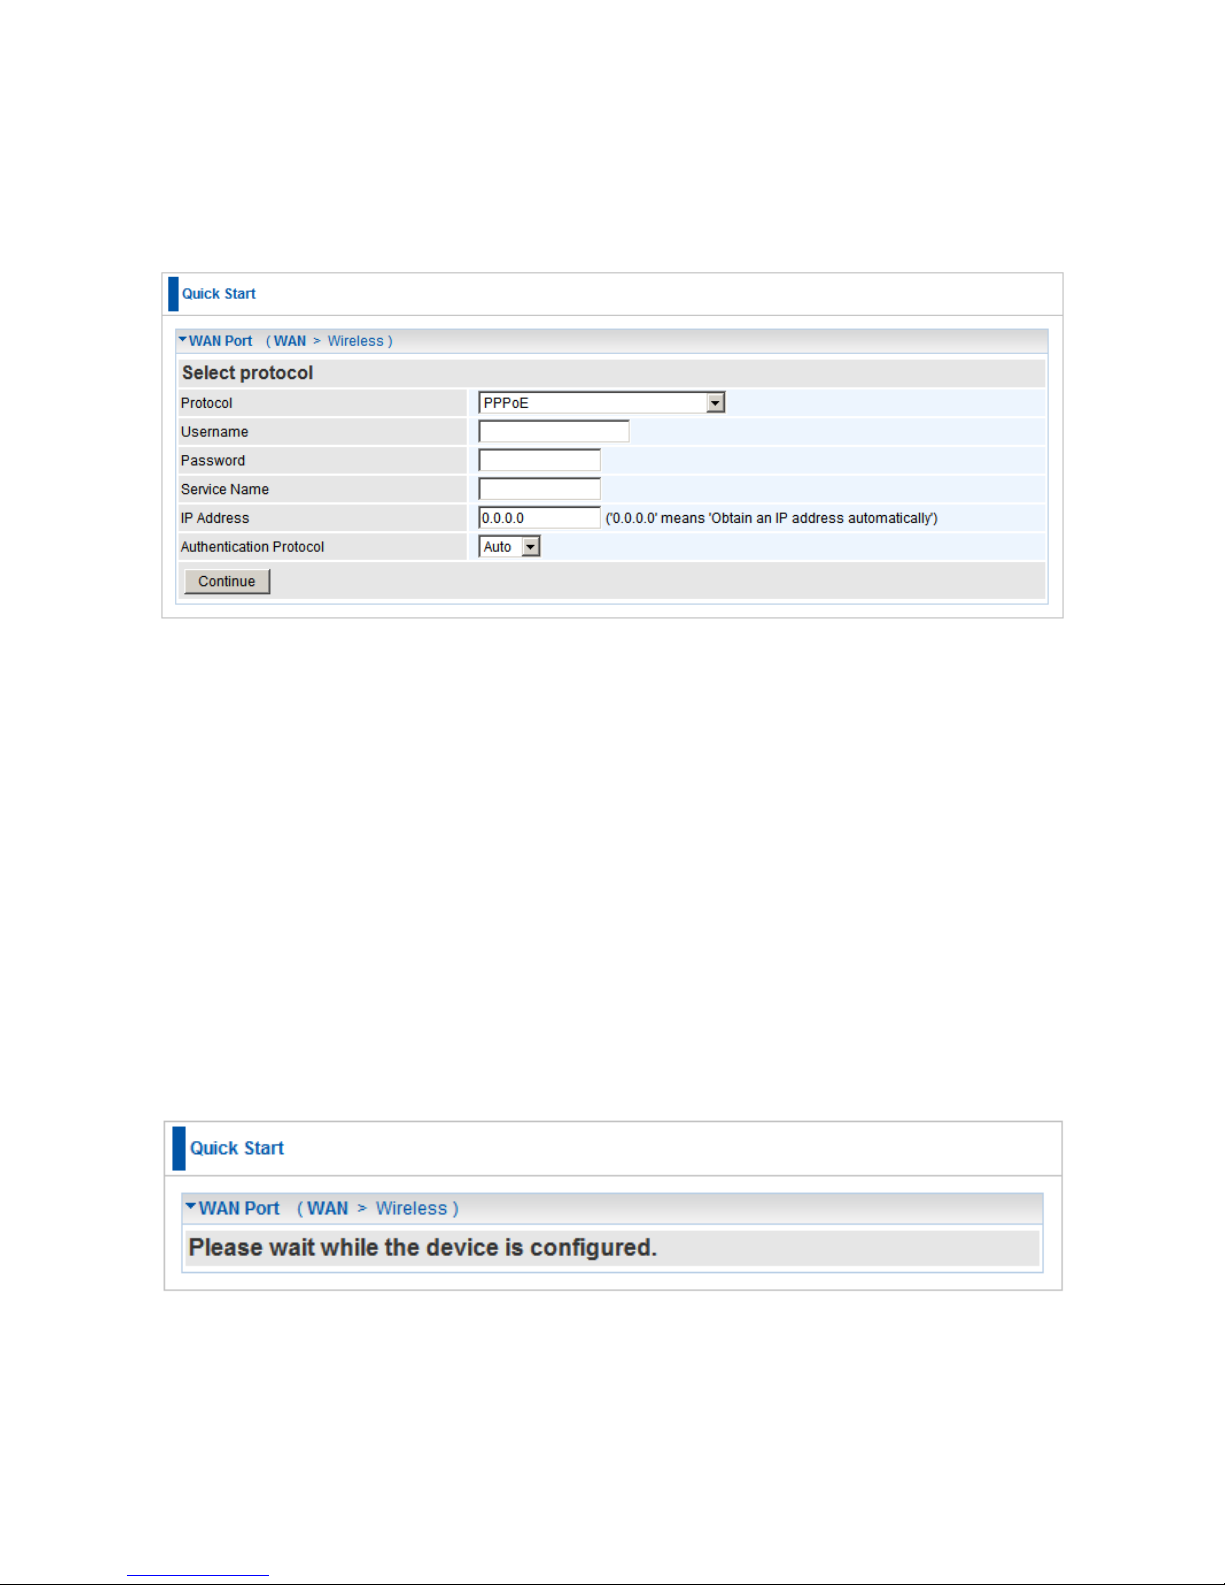
PPPoE
PPPoE (PPP over Ethernet) provides access control in a manner similar to dial-up
services using PPP.
Protocol: The current ATM protocol in the device
Username: Enter the username provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive). This is in the format of
“username@ispname” instead of simply “username”.
Password: Enter the password provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive).
Service Name: Enter a name for this connection.
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Auth. Protocol: Default is Auto. Your ISP advises on using Chap or Pap.
Click on the Continue button and wait for your connection to be connected.
Page 55
55
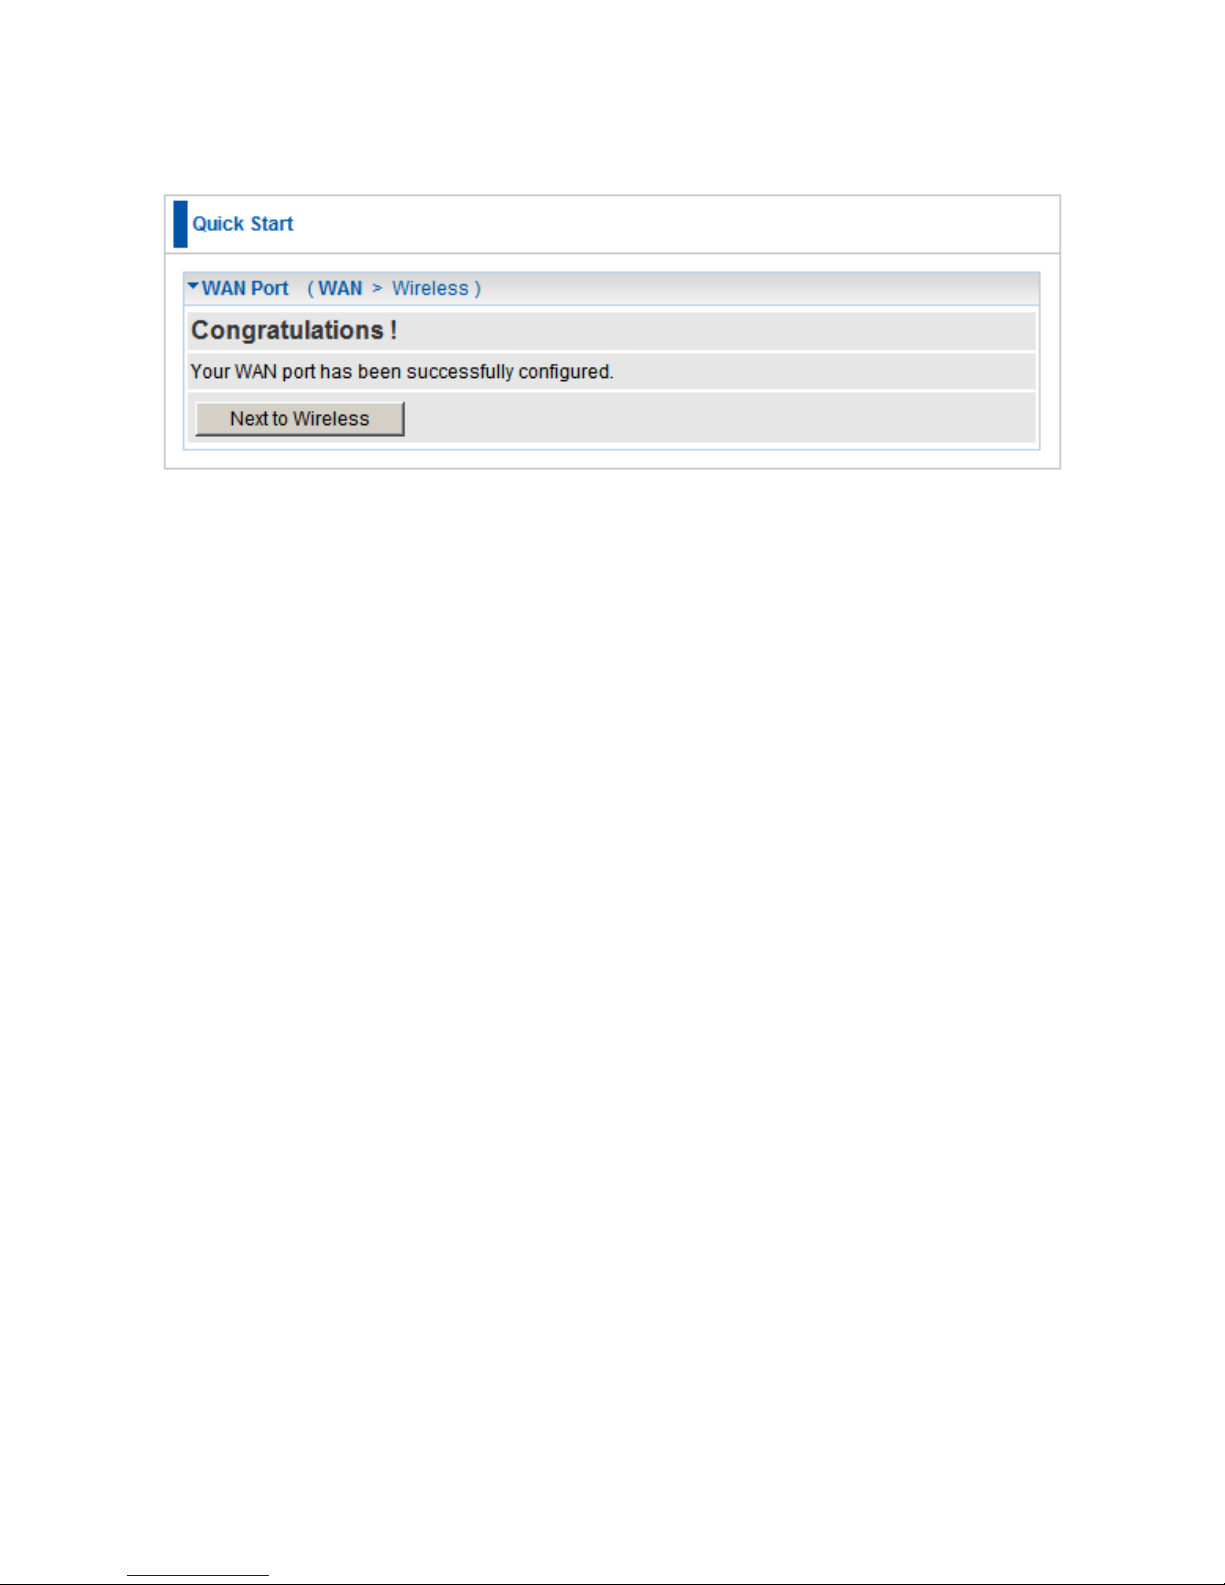
If connection is successful the following image will be shown.
Page 56
56
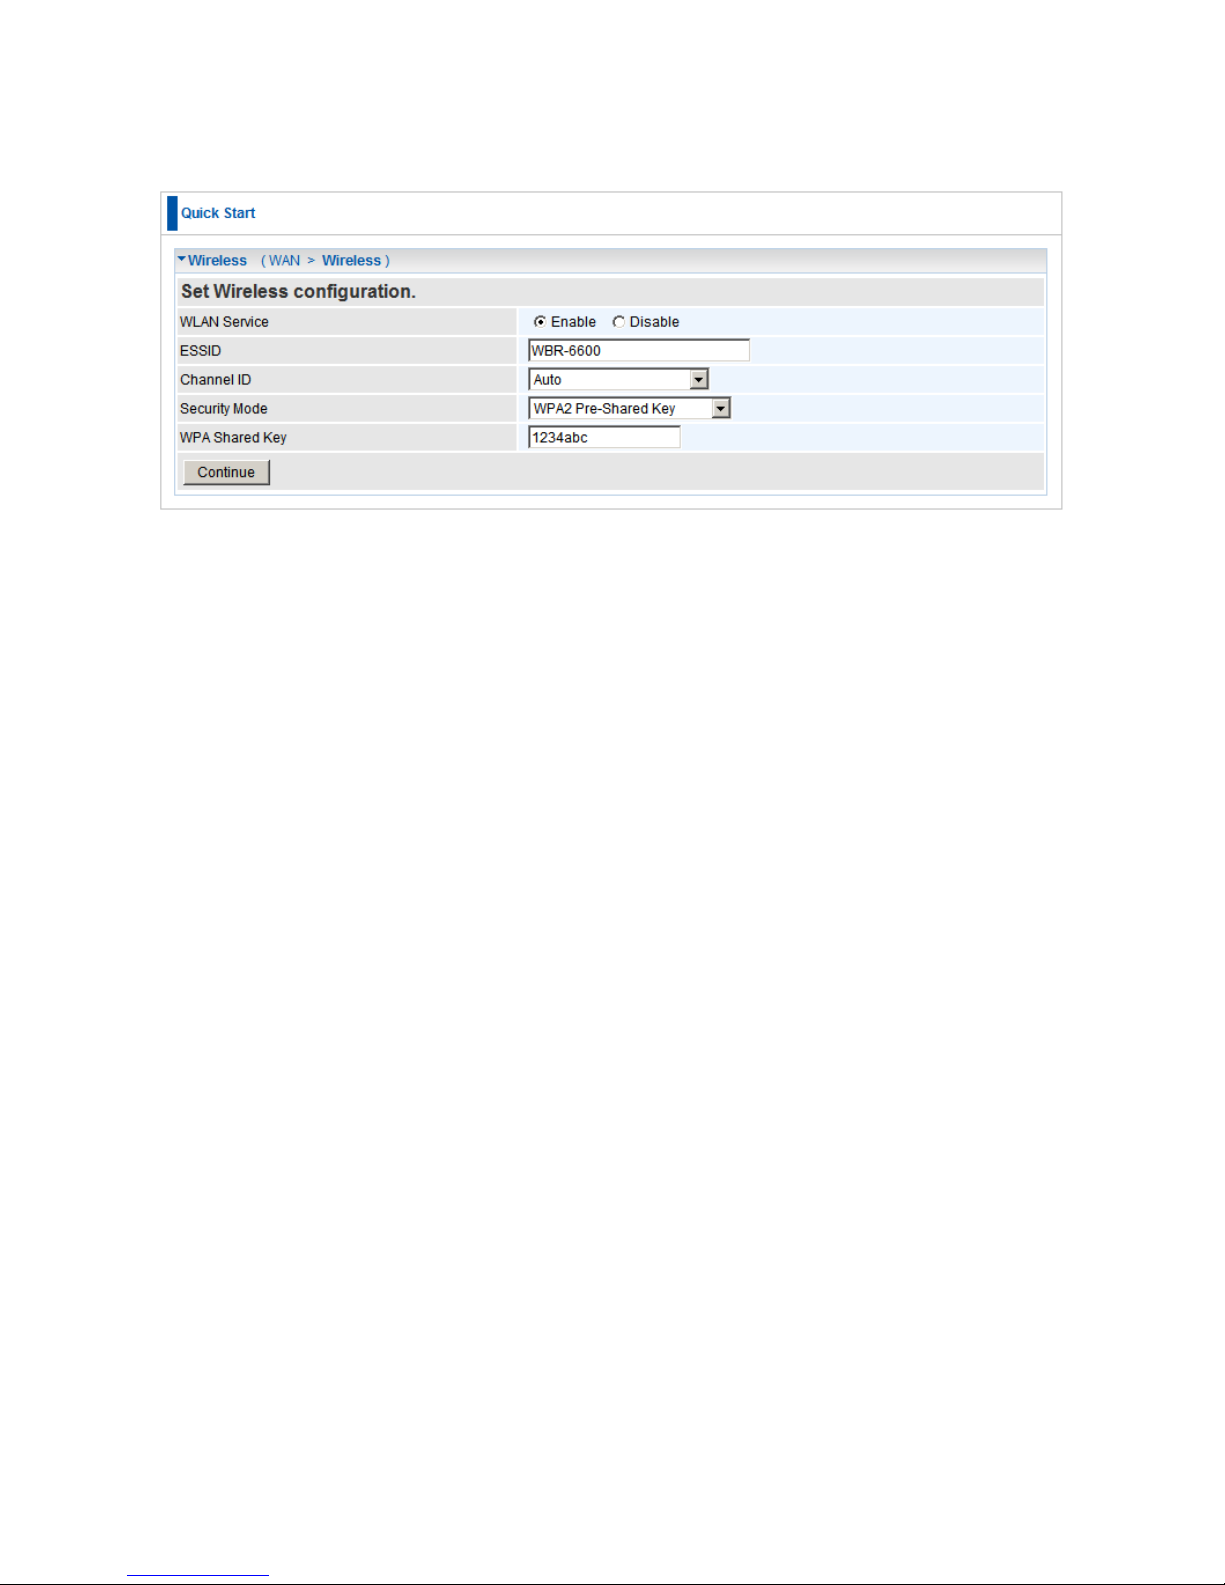
Set Wireless Configuration
WLAN Service: Default setting is set to Enable.
ESSID: The ESSID is the unique name of a wireless access point (AP) to be
distinguished from another. For security purpose, change to a unique ID name to the
AP which is already built-in to the router‟s wireless interface. It is case sensitive and
must not excess 32 characters. Make sure your wireless clients have exactly the
ESSID as the device, in order to get connected to your network.
Channel ID: Select the ID channel that you would like to use. (Recommend Auto)
Security Mode: You can disable or enable with WPA or WEP for protecting wireless
network. The default mode of wireless security is Disable.
Page 57
57
Configuration
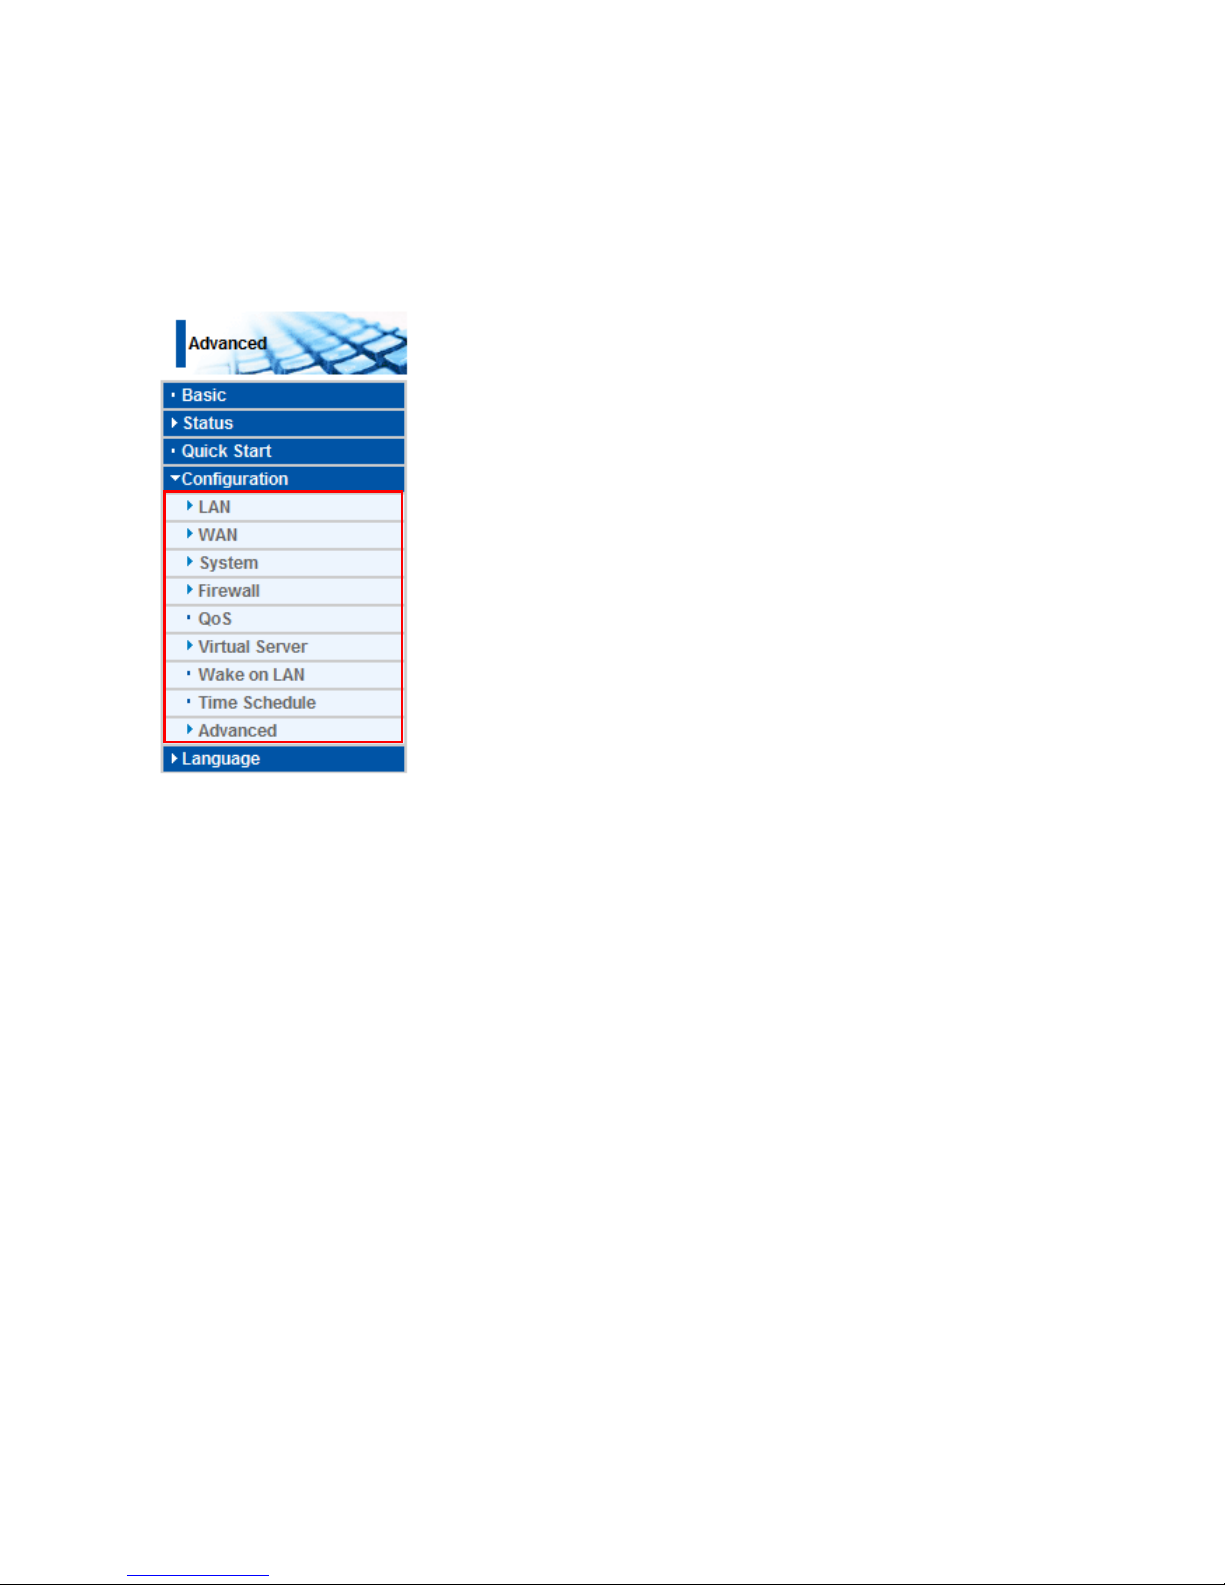
Click this item to access the following sub-items that configure the ADSL router: LAN, WAN,
System, Firewall, QoS, Virtual Server, Wake on LAN, Time Schedule and Advanced.
These functions are described in the following sections.
Page 58
58
LAN (Local Area Network)
A Local Area Network (LAN) is a shared communication system to which many computers
are attached and is limited to the immediate area, usually the same building or floor of a
building.
There are six items within the LAN section: Ethernet, IP Alias, Wireless, Wireless
Security, and DHCP Server.
Page 59
59
Ethernet
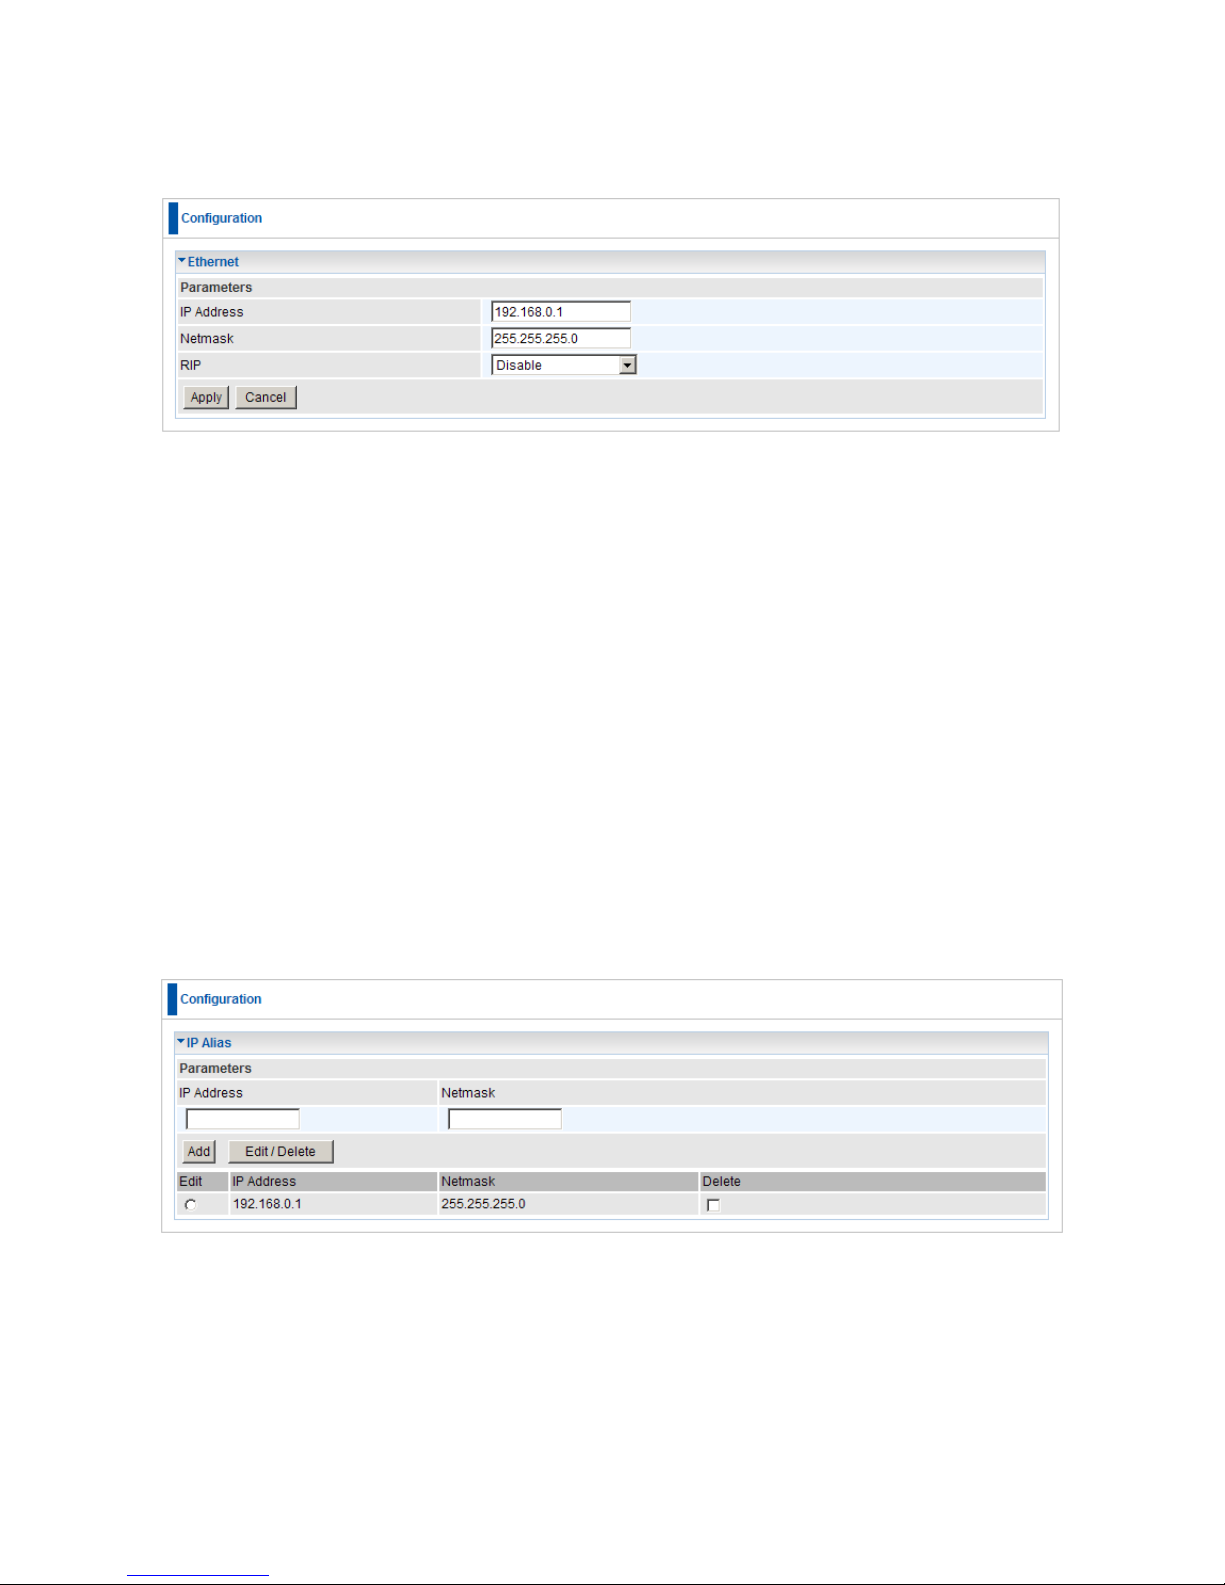
The router supports more than one Ethernet IP addresses in the LAN, and with distinct
LAN subnets through which you can access the Internet at the same time. Users usually
only have one subnet in their LAN. The default IP address for the router is 192.168.0.1.
IP Address: The LAN IP address of this router.
Netmask: The LAN subnet mask of this router.
RIP: RIP v1, RIP v2 Broadcast, RIP v2 Multicast and RIP v1+v2 Broadcast.
IP Alias
This function allows the creation of multiple virtual IP interfaces on this router. It helps to
connect two or more local networks to the ISP or remote node. In this case, an internal
router is not required.
You can set up to five IP Alias‟s.
IP Address: Specify an IP address on this virtual interface.
Netmask: Specify a subnet mask on this virtual interface.
Page 60
60
Wireless
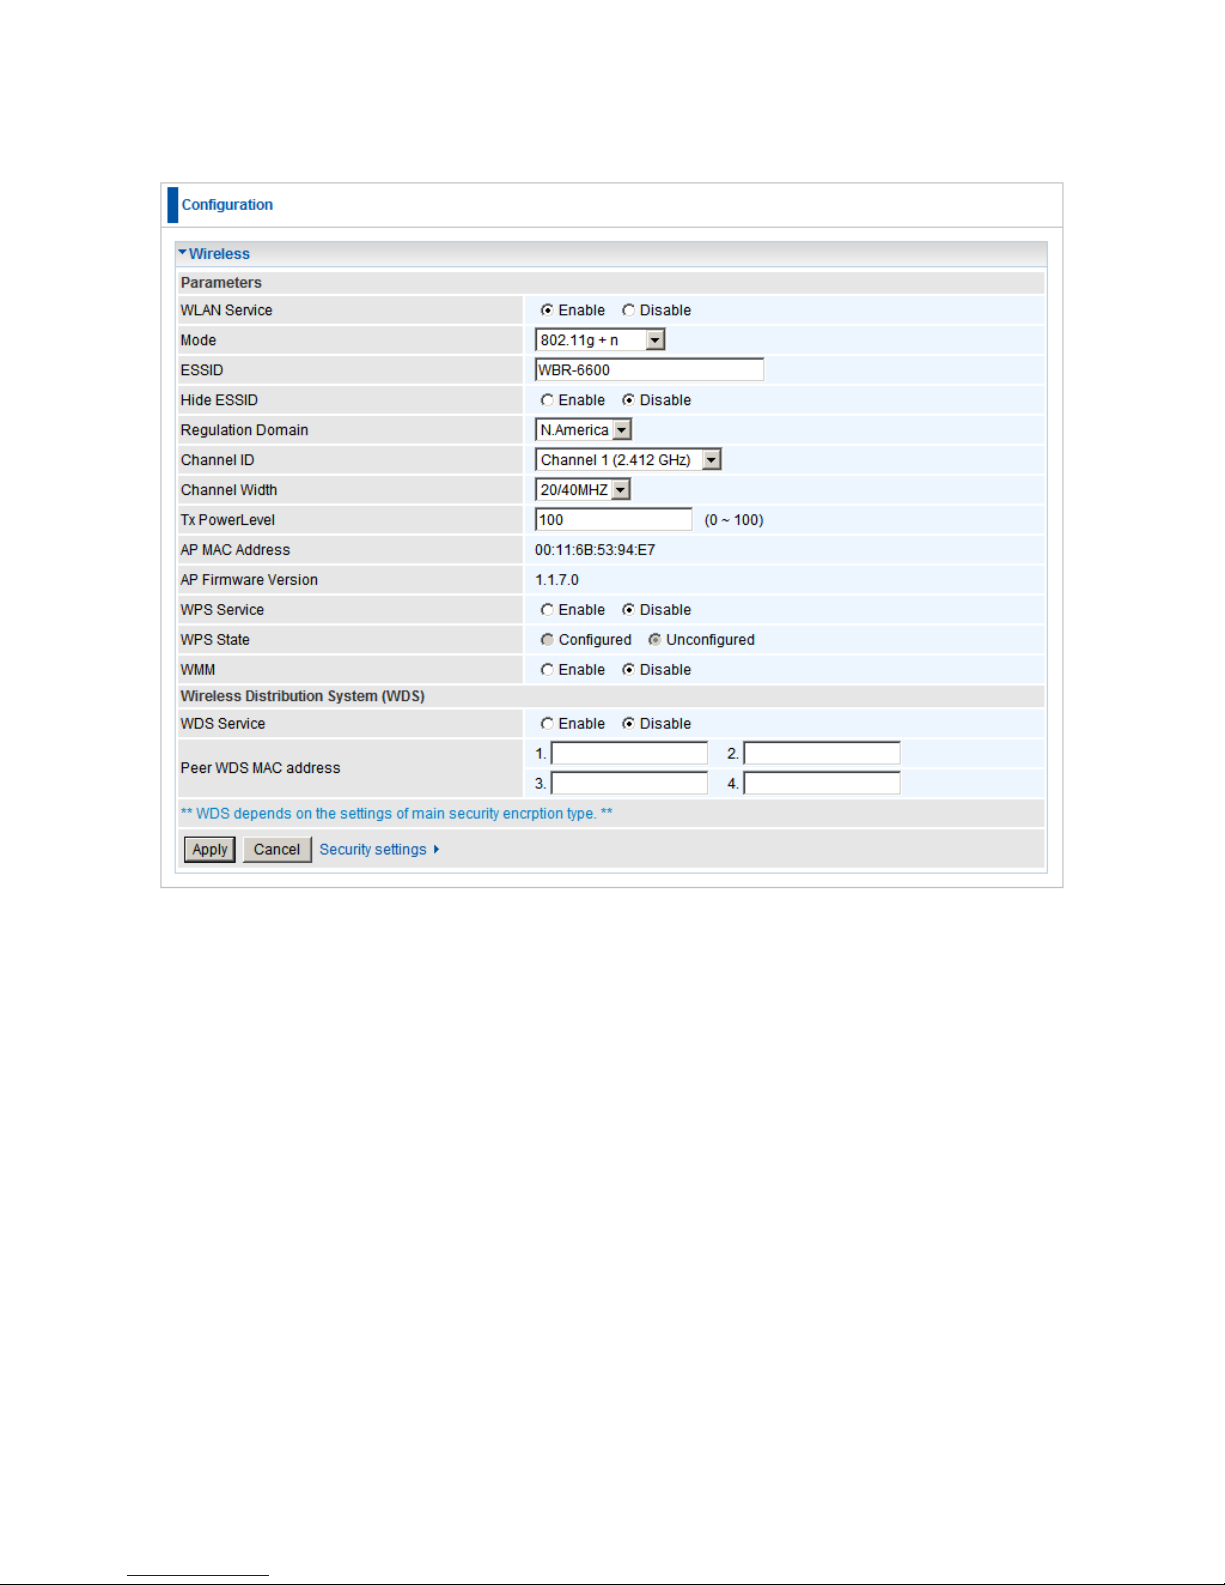
WLAN Service: Choose to Enable or Disable the Wireless Network. Default setting is
set to Enable.
Mode: The default setting is 802.11g+n (Mixed mode). If you do not know or have both
11g and 11n devices in your network, then keep the default in mixed mode. From the
drop-down manual, you can select 802.11g if you have only 11g card. If you have only
11b card, then select 802.11b. If you have only 11n card, then select 802.11n.
ESSID: The ESSID is the unique name of a wireless access point (AP) to be
distinguished from another. For security propose, change to a unique ID name to the
AP which is already built-in to the router‟s wireless interface. It is case sensitive and
must not excess 32 characters. Make sure your wireless clients have exactly the
ESSID as the device, in order to get connected to your network.
Note: ESSID is case sensitive and must not excess 32 characters.
Page 61
61
Hide ESSID: It is function in which transmits its ESSID to the air so that when wireless
client searches for a network, router can then be discovered and recognized. Default
setting is Disable.
o Enable: Select Enable if you do not want broadcast your ESSID. When select
Enable, no one will be able to locate the Access Point (AP) of your router.
o Disable: When Disable is selected, you can allow anybody with a wireless
client to be able to locate the Access Point (AP) of your router.
Regulation Domain: There are seven Regulation Domains for you to choose from,
including North America (N.America), Europe, France, etc. The Channel ID will be
different based on this setting.
Channel ID: Select the ID channel that you would like to use.
Tx Power Level: It is function that enhances the wireless transmitting signal strength.
User may adjust this power level from minimum 0 up to maximum 100.
Note: The Power Level maybe different in each access network user premises
environment and choose the most suitable level for your network.
AP MAC Address: It is a unique hardware address of the Access Point.
AP Firmware Version: The Access Point firmware version.
WPS service: Enable / disable
WPS State: Current WPS state in AP. It is be used for Microsoft Windows Connect
Now (WCN).
o Configured: This AP is be configured via WPS. It is not allow to be configured
WCN.
o Unconfigured: This AP is un-configured via WPS. It can be configured via
WCN.
Page 62
62
Wireless Distribution System (WDS)
It is a wireless access point mode that enables wireless link and communication with
other access point. It is easy to be installed, simply define the peer‟s MAC address of the
connected AP. WDS takes advantages of cost saving and flexibility which no extra
wireless client device is required to bridge between two access points and extending an
existing wired or wireless infrastructure network to create a larger network.
WDS Service: The default setting is Disable. Check Enable radio button to activate this
function.
Note: Only WEP Encryption will work with WDS function.
Peer WDS MAC Address: It is the associated AP‟s MAC Address. It is important that
your peer‟s AP must include your MAC address in order to acknowledge and
communicate with each other.
Please enter the MAC addresses of the Access Points you wish to inter-connect using
the WDS function.
Note: For MAC Address, Semicolon ( : ) or Dash (-) must be included.
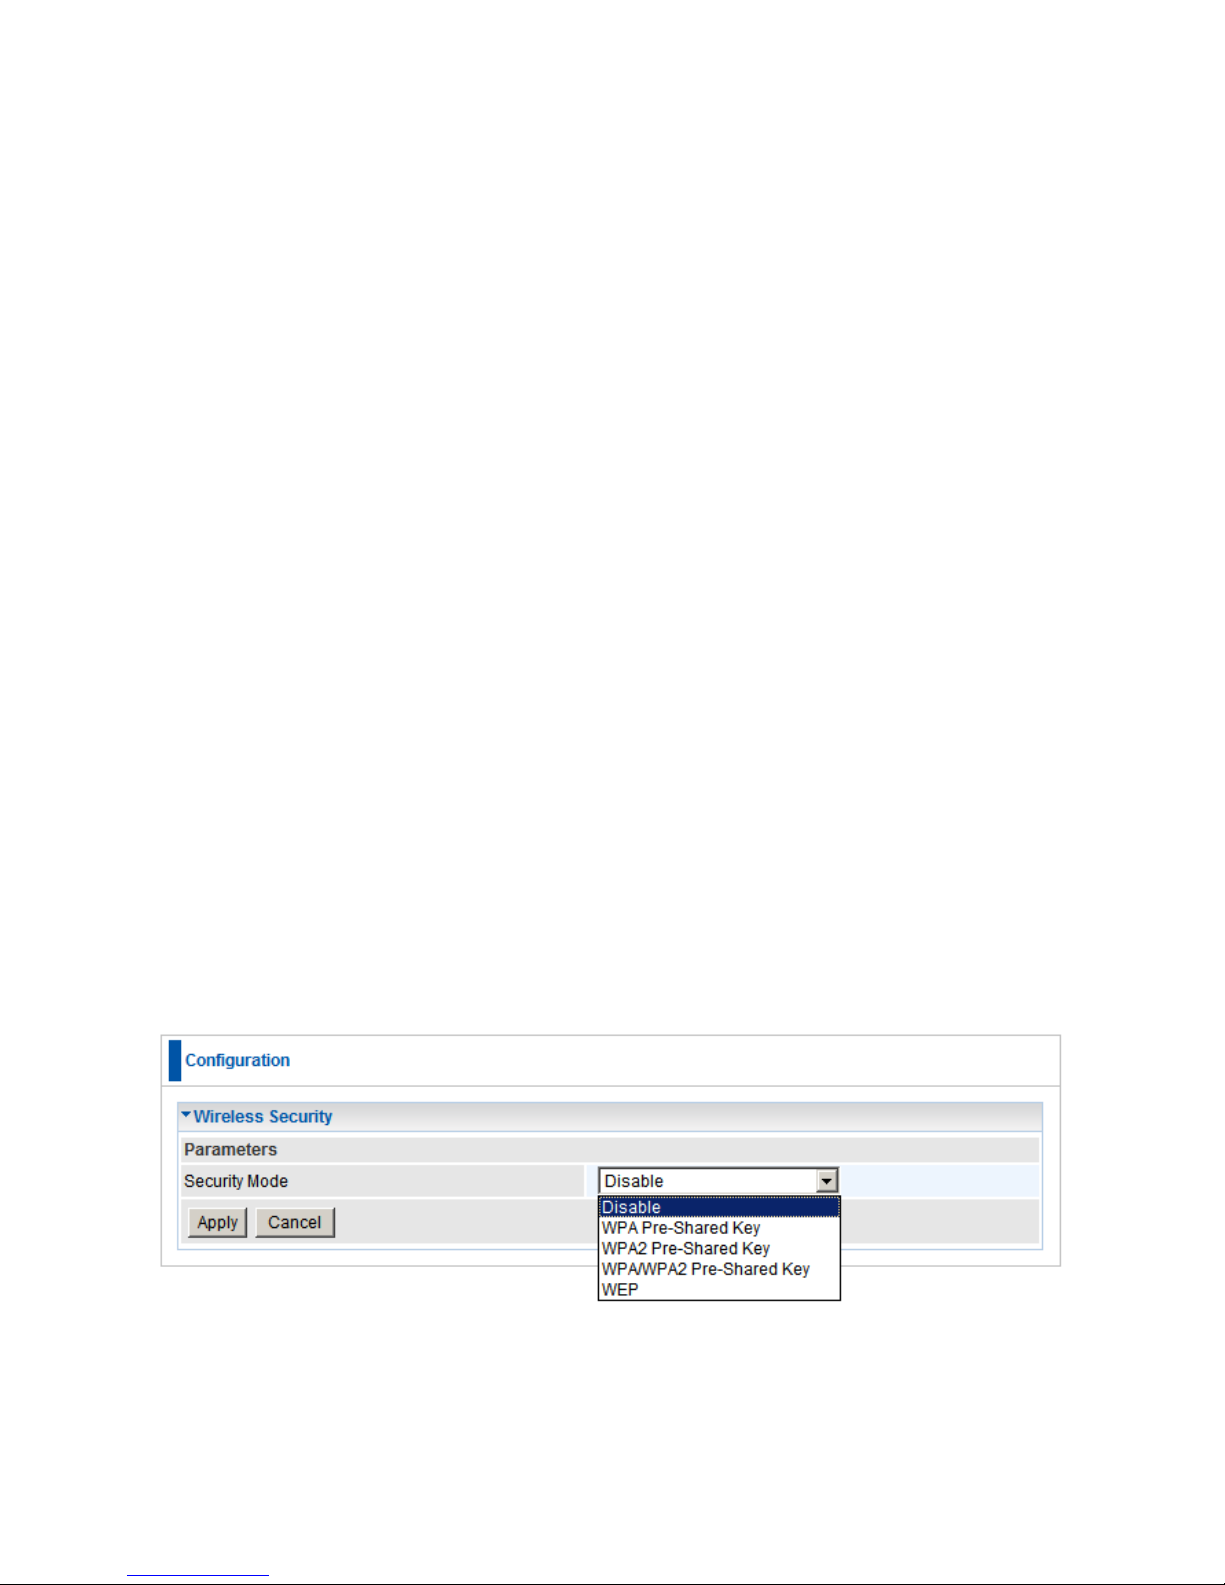
Wireless Security
You can disable or enable with WPA, WPA2 or WEP for protecting wireless network. The
default mode of wireless security is Disable.
LevelOne recommends WPA2 for maximum security.
Page 63
63
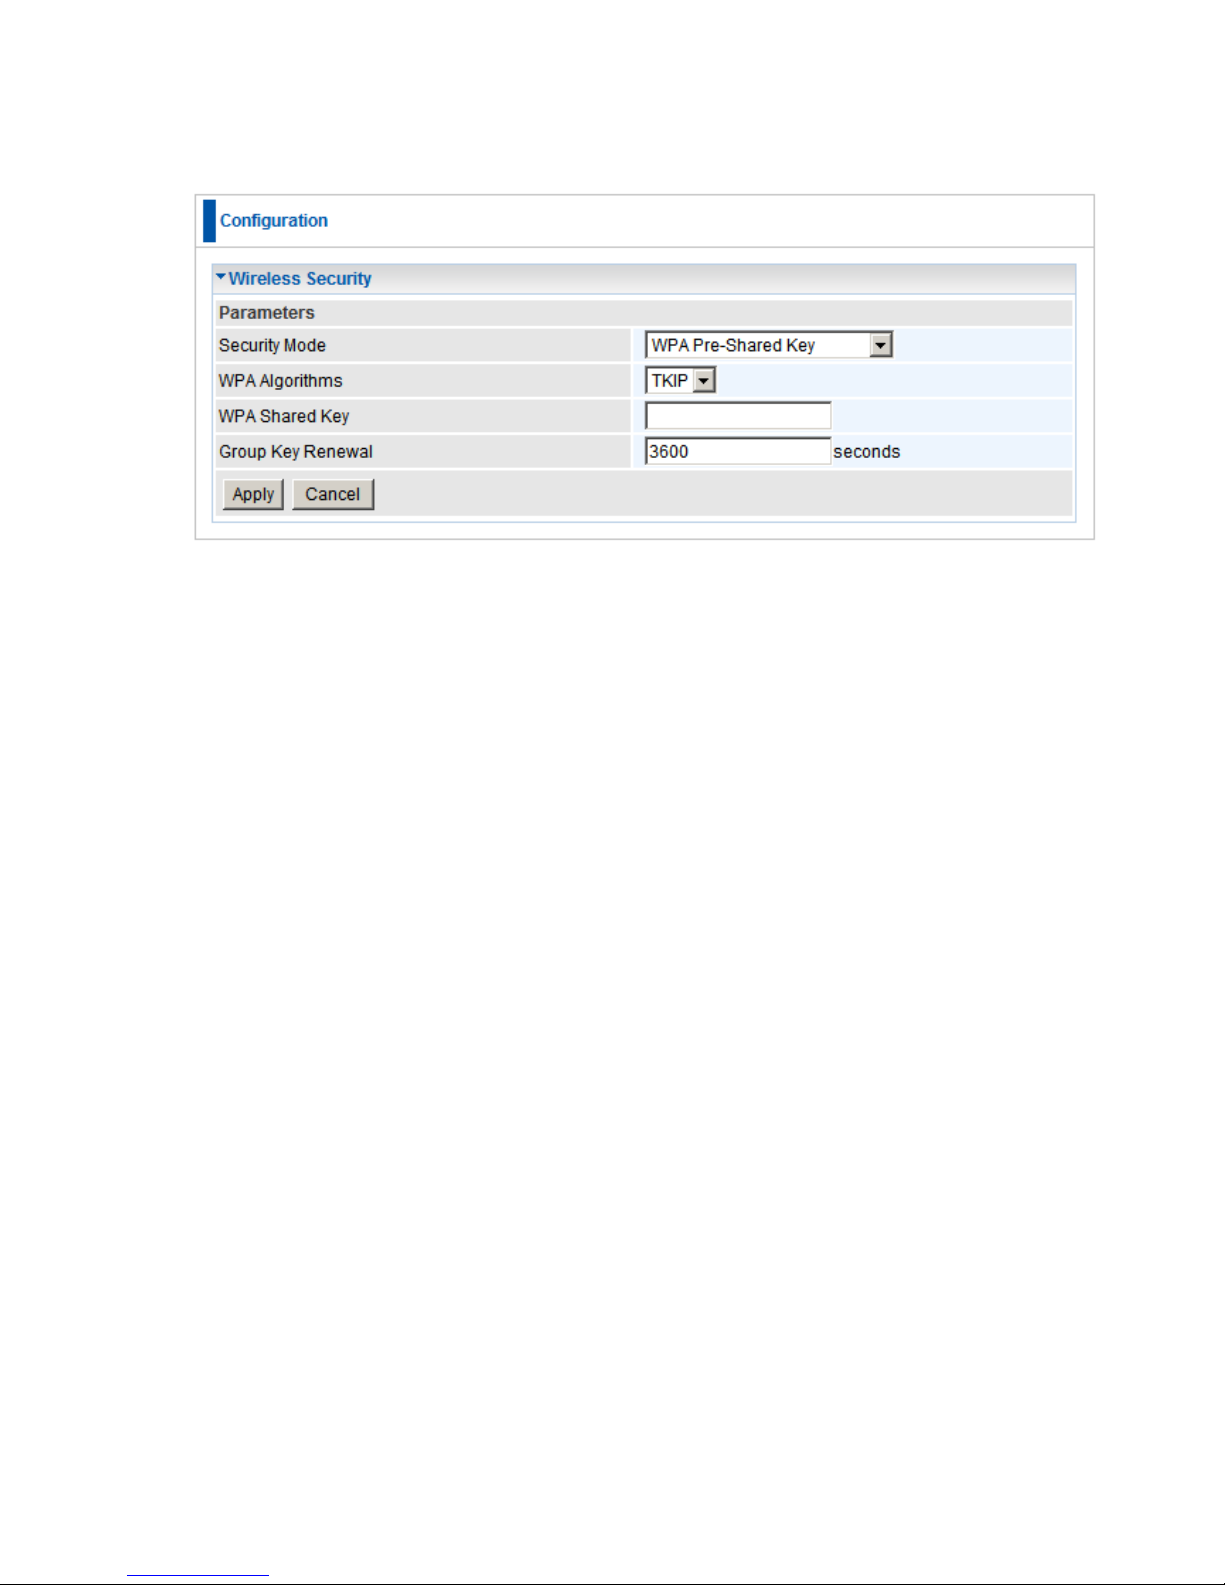
WPA Pre-Shared Key
WPA Algorithms: The type of encryption used.
TKIP (Temporal Key Integrity Protocol)
AES (Advanced Encryption Standard) utilizes a stronger encryption method then TKIP
and incorporates Message Integrity Code (MIC) to provide protection against hackers.
WPA Shared Key: The key for network authentication. The input format is in character
style and key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
automatically between wireless client and Access Point (AP).
Page 64
64
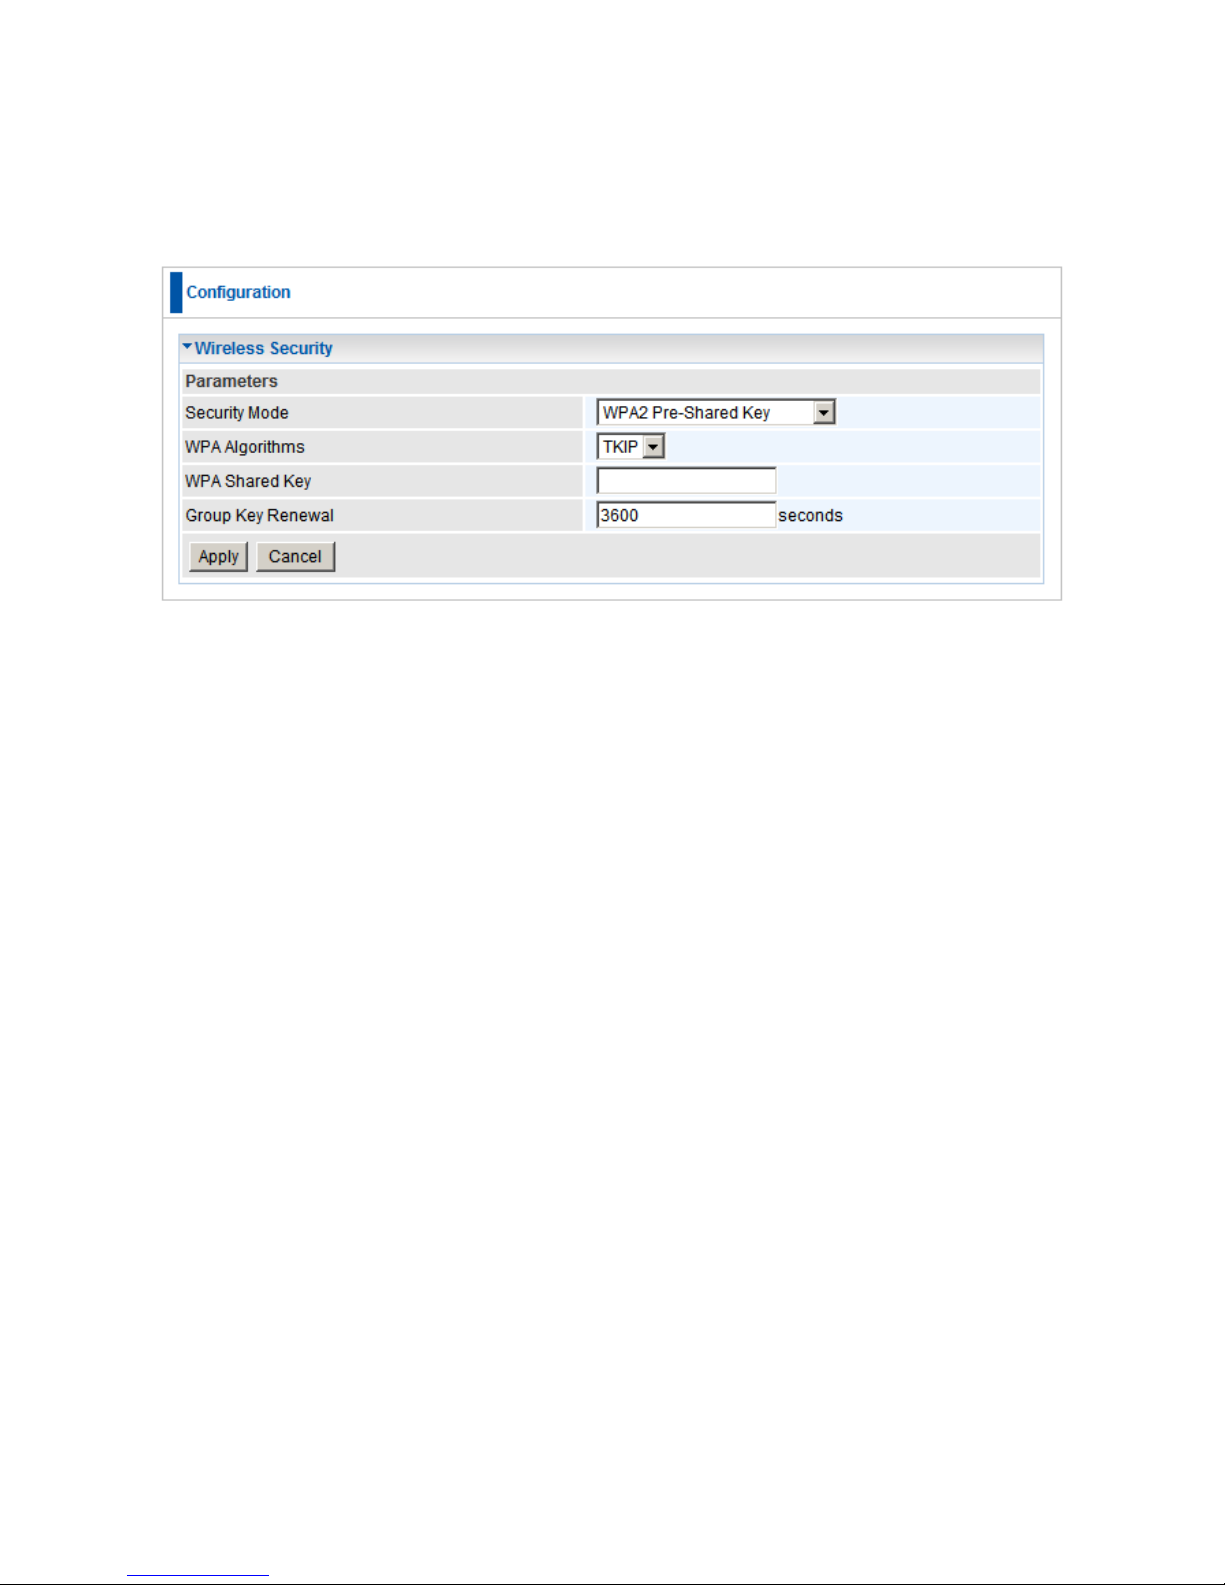
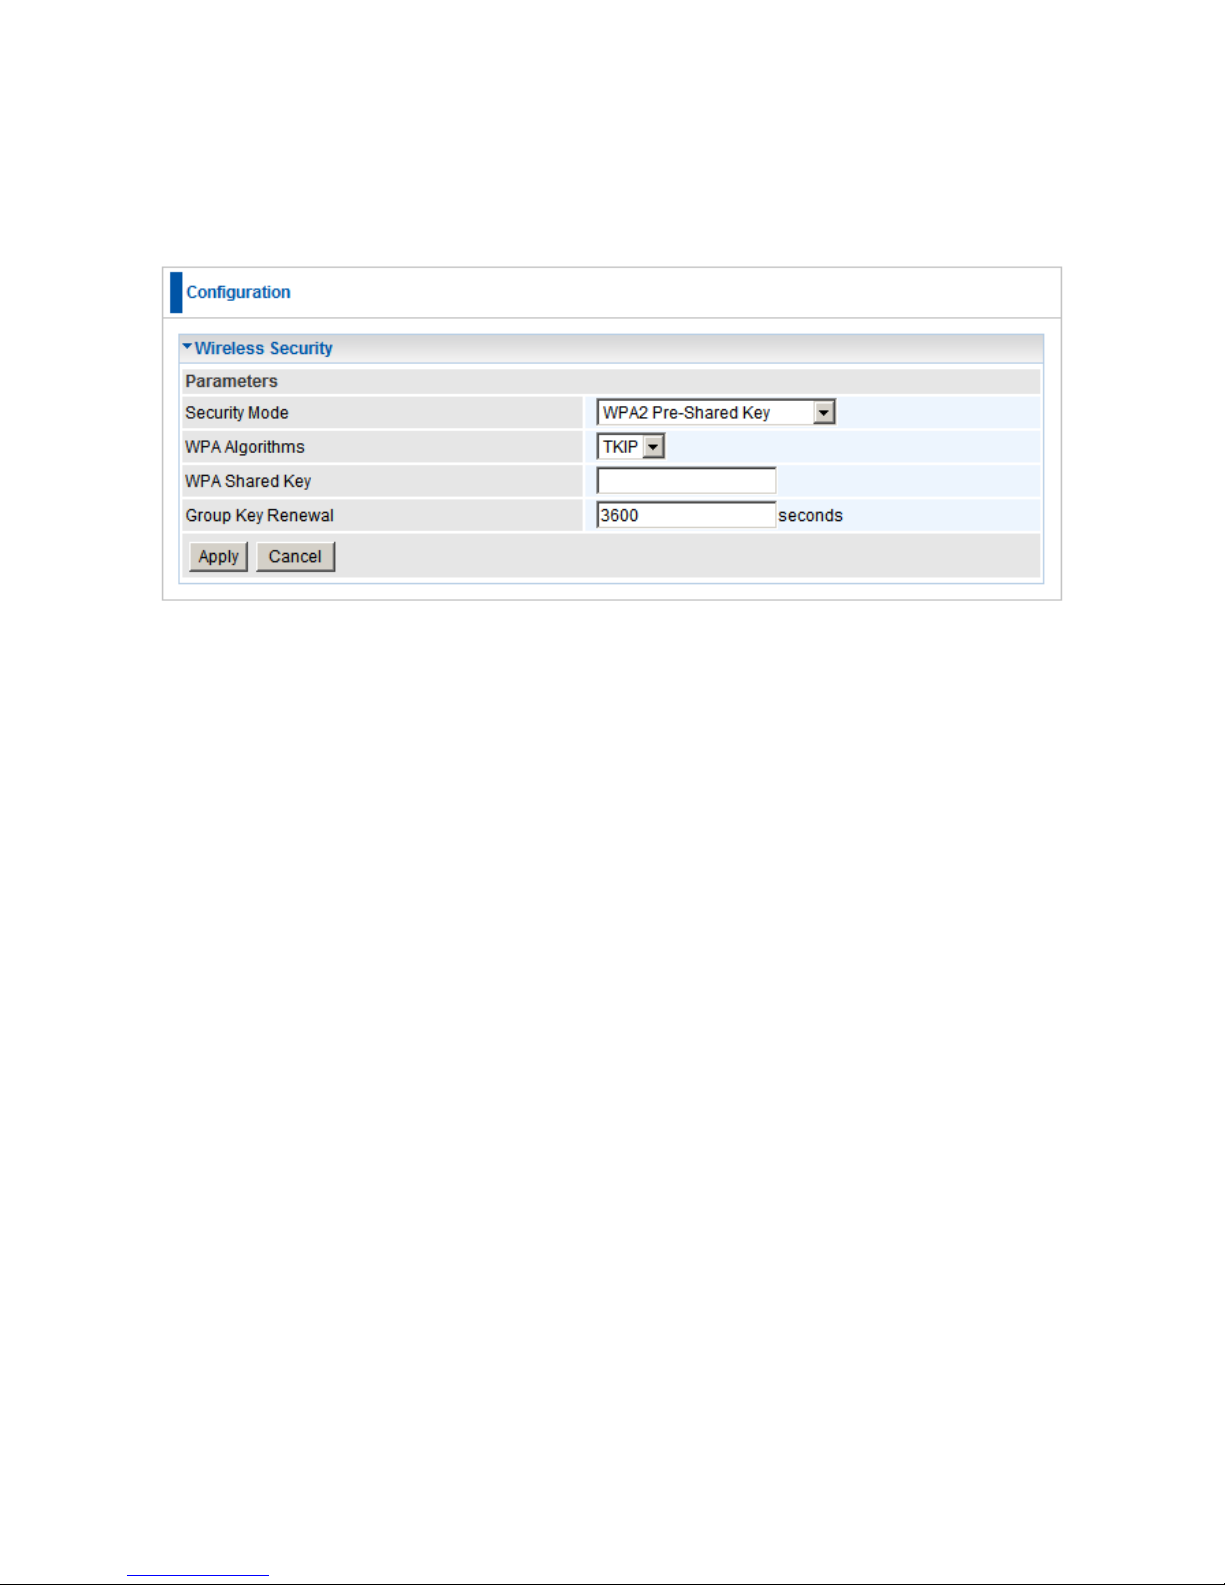
WPA2 Pre-Shared Key
WPA2 is a more advanced and secure form of encryption. The most secure form of
wireless security is WPA2 with AES algorithms.
WPA Algorithms: The type of encryption used.
TKIP (Temporal Key Integrity Protocol)
AES (Advanced Encryption Standard) utilizes a stronger encryption method than TKIP
and incorporates Message Integrity Code (MIC) to provide protection against hackers.
WPA2 Shared Key: The key for network authentication. The input format is in character
style and key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
automatically between wireless client and Access Point (AP).
Page 65
65
WPA/WPA2 Pre-Shared Key
This mode allows the WBR-6600 to accept wireless clients using both WPA and WPA2
encryptions.
WPA Algorithms: The type of encryption used.
TKIP (Temporal Key Integrity Protocol)
AES (Advanced Encryption Standard) utilizes a stronger encryption method than TKIP
and incorporates Message Integrity Code (MIC) to provide protection against hackers.
WPA Shared Key: The key for network authentication. The input format is in character
style and key size should be in the range between 8 and 63 characters.
Group Key Renewal: The period of renewal time for changing the security key
automatically between wireless client and Access Point (AP).
Page 66
66
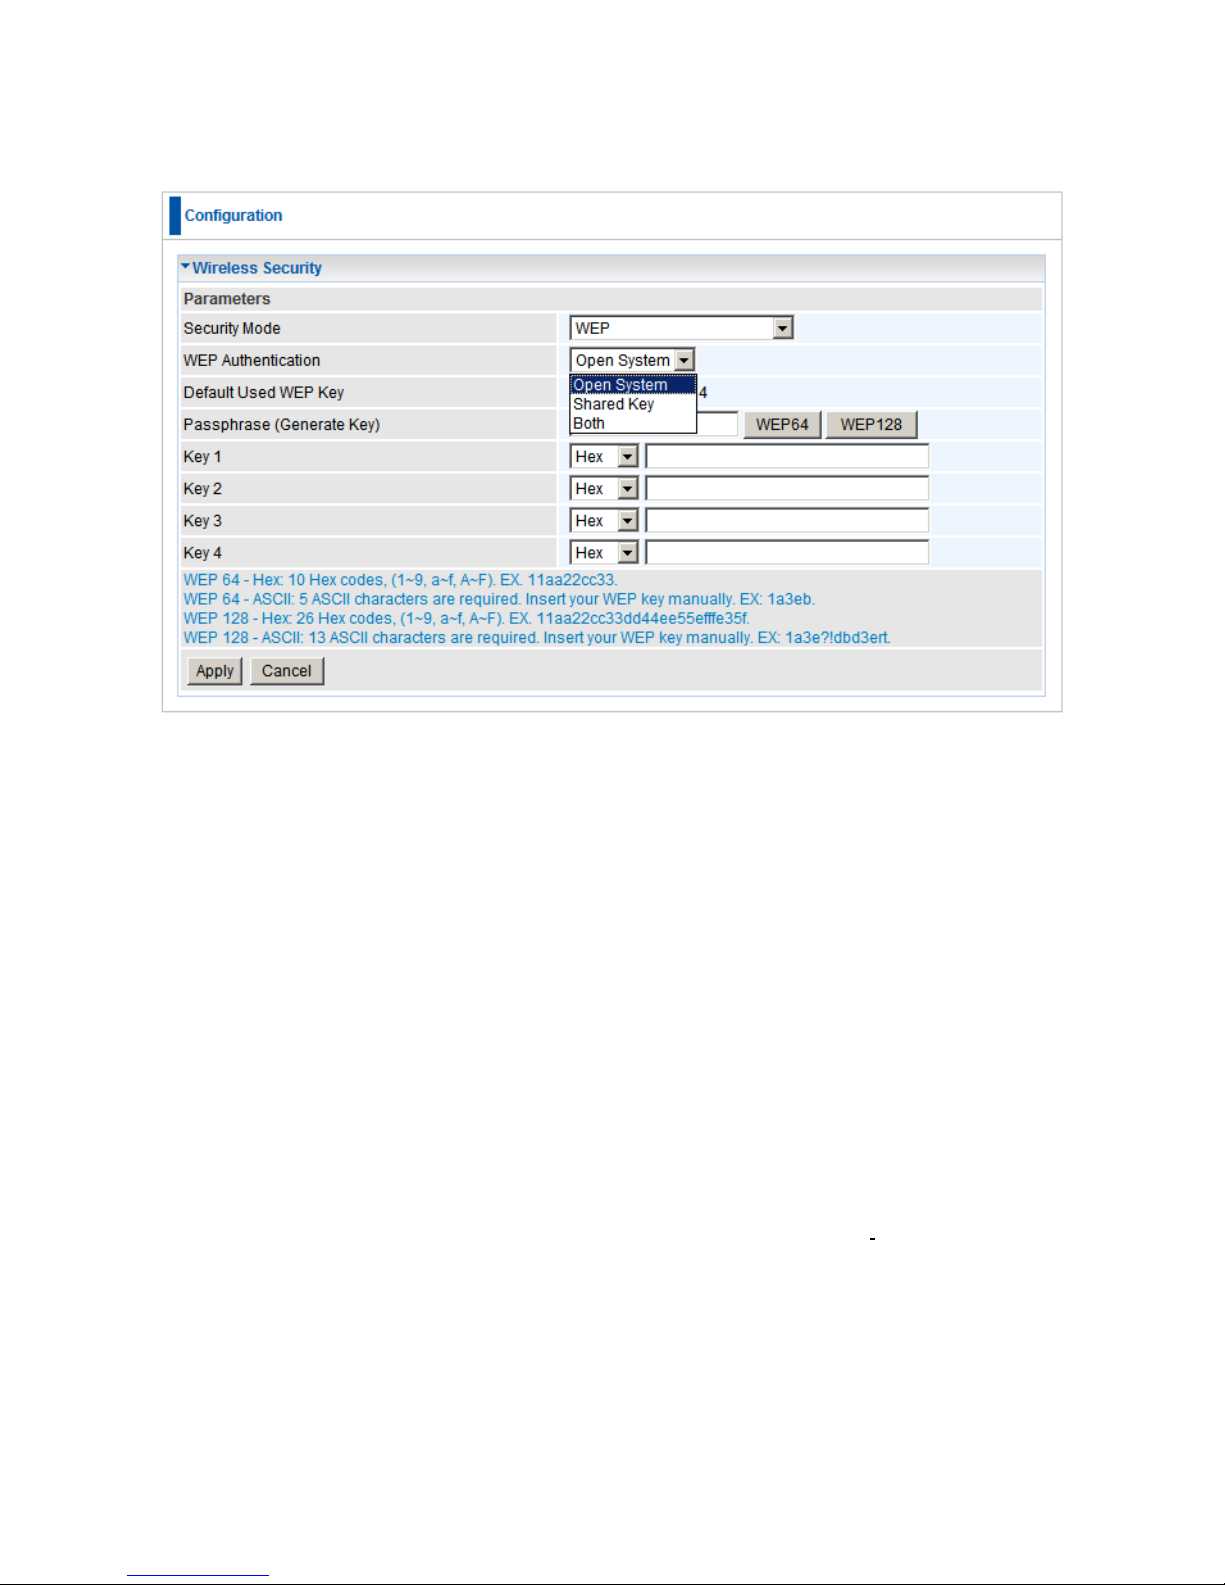
WEP
WEP Authentication: To prevent unauthorized wireless stations from accessing data
transmitted over the network, the router offers secure data encryption, known as WEP.
If you require high security for transmissions, there are three options to select from:
Open System, Share key or Both.
Default Used WEP Key: Select the encryption key ID; please refer to Key (1~4)
below.
Passphrase: This is used to generate WEP keys automatically based upon the input
string and a pre-defined algorithm in WEP64 or WEP128. You can input the same
string in both the AP and Client card settings to generate the same WEP keys. Please
note that you do not have to enter Key (1-4) as below when the Passphrase is
enabled.
Key (1-4): Enter the key to encrypt wireless data. To allow encrypted data transmission,
the WEP Encryption Key values on all wireless stations must be the same as the router.
There are four keys for your selection. The input format is in HEX or ASCII style, 5 and
13 ASCII codes are required for WEP64 and WEP128 respectively no any separator is
included.
Page 67
67
Wi-Fi Protected Setup (WPS)
WPS feature is following the Wi-Fi Alliance WPS standard and it eases the set up of
security-enabled Wi-Fi networks in the home and small office environment.
It reduces the user steps required to configure a network and supports two methods that
are familiar to most consumers to configure a network and enable security.
All devices supporting WPS can be set up either as Registrar or Enrollee.
o Registrar – The device that allocates the security criteria‟s such as encryption
method and passphrases.
o Enrollee – The device that accepts and uses the security criteria‟s given by the
registrar.
Page 68
68
Set up WBR-6600 as WPS Registrar
Using the Registrar mode, it means that the WBR-6600 will be allocating the wireless
security parameters such as encryption method and passphrase.
There are two methods of connecting the WBR-6600 router to wireless devices using
WPS. They are the Push Button Method and the PIN Code Method.
Push Button Method is to either press the physical WPS buttons on the WPS
devices, or click the Push Button Configuration (PBC) button in the software
utility.
PIN Code Method to use the software utility to authenticate using a PIN code.
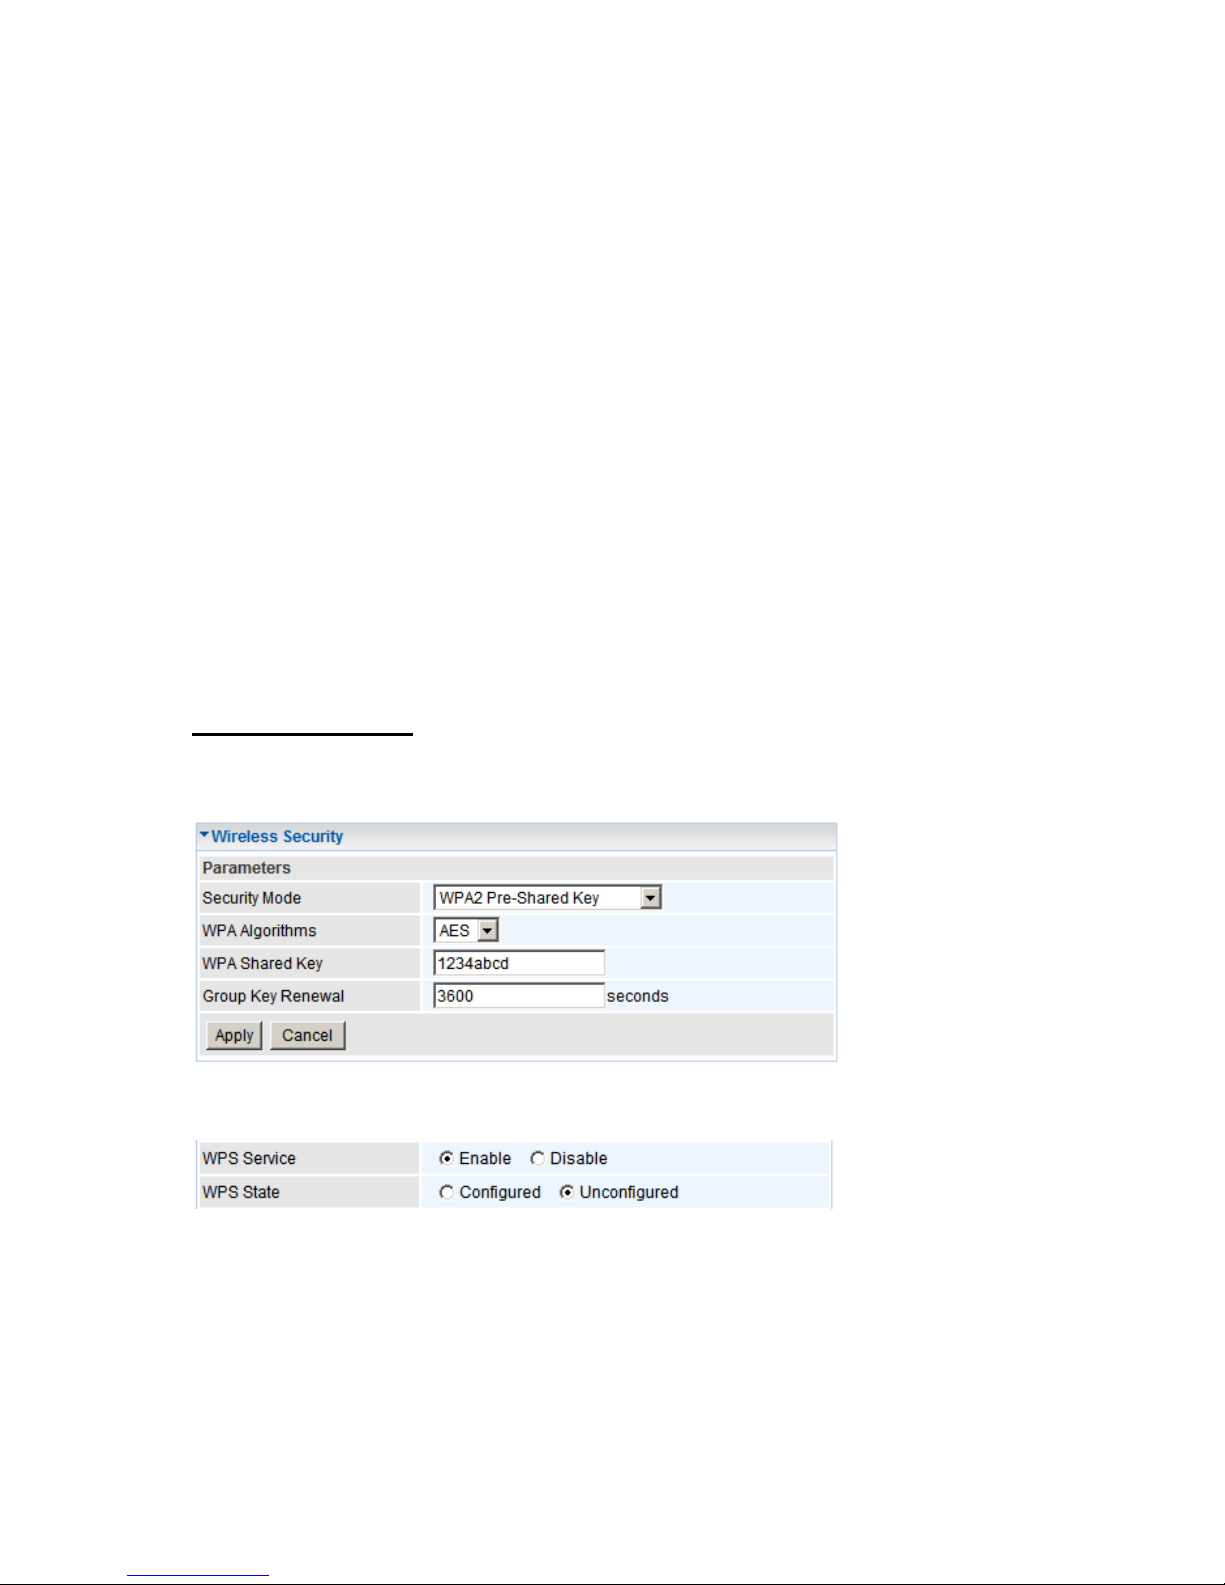
When using WPS as a registrar for the first time, please set up your wireless security
settings first. See page 57.
Push Button Method
1. First make sure wireless security settings are set up.
2. Ensure WPS is enabled on the Wireless settings page.
Page 69
69
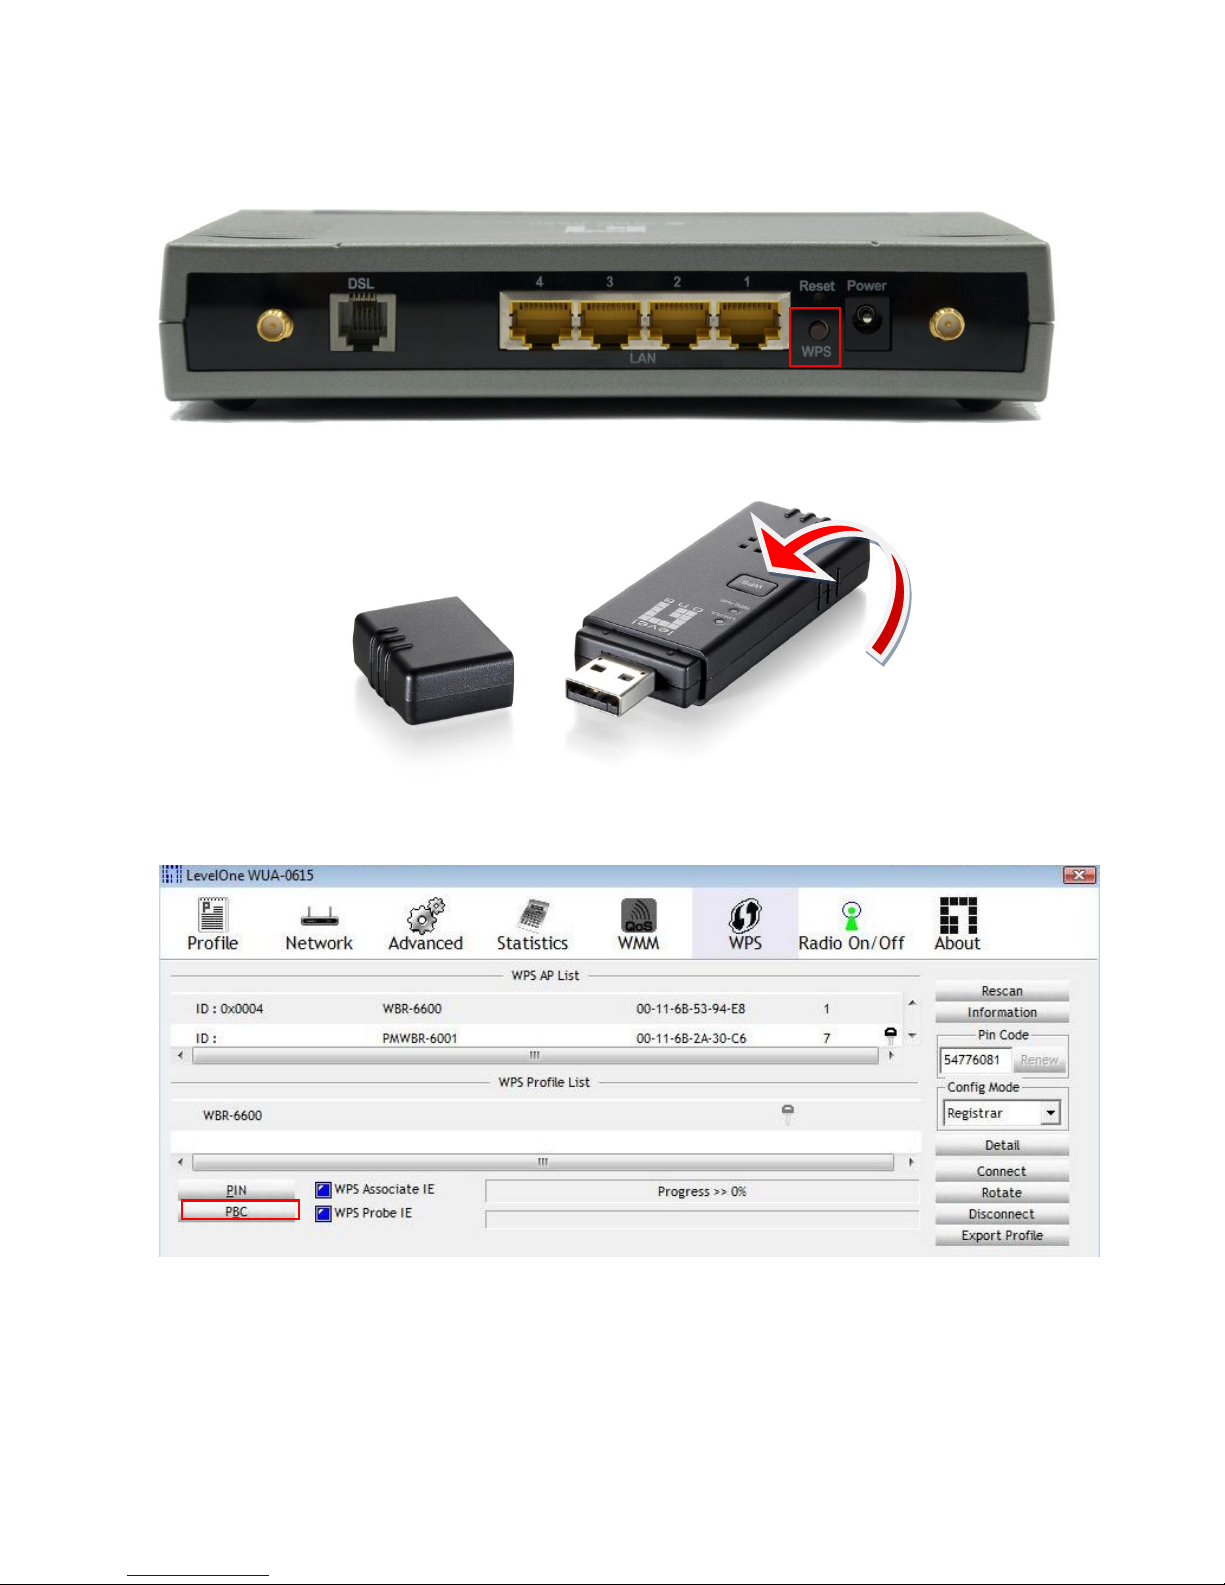
3. Press and hold the WPS button at the rear of the WBR-6600 for 1 second.
4. Press and hold the WPS button on your wireless client for 1 second.
If your device has no physical WPS push button, then you can push the software
button in the utility.
Note: Above screenshot is from LevelOne’s WUA-0600 and WUA-0615. Other
wireless adapters may be different.
5. The wireless client should now have implemented the security settings on the
WBR-6600 and successfully achieved a connection.
Page 70
70
PIN Code Method
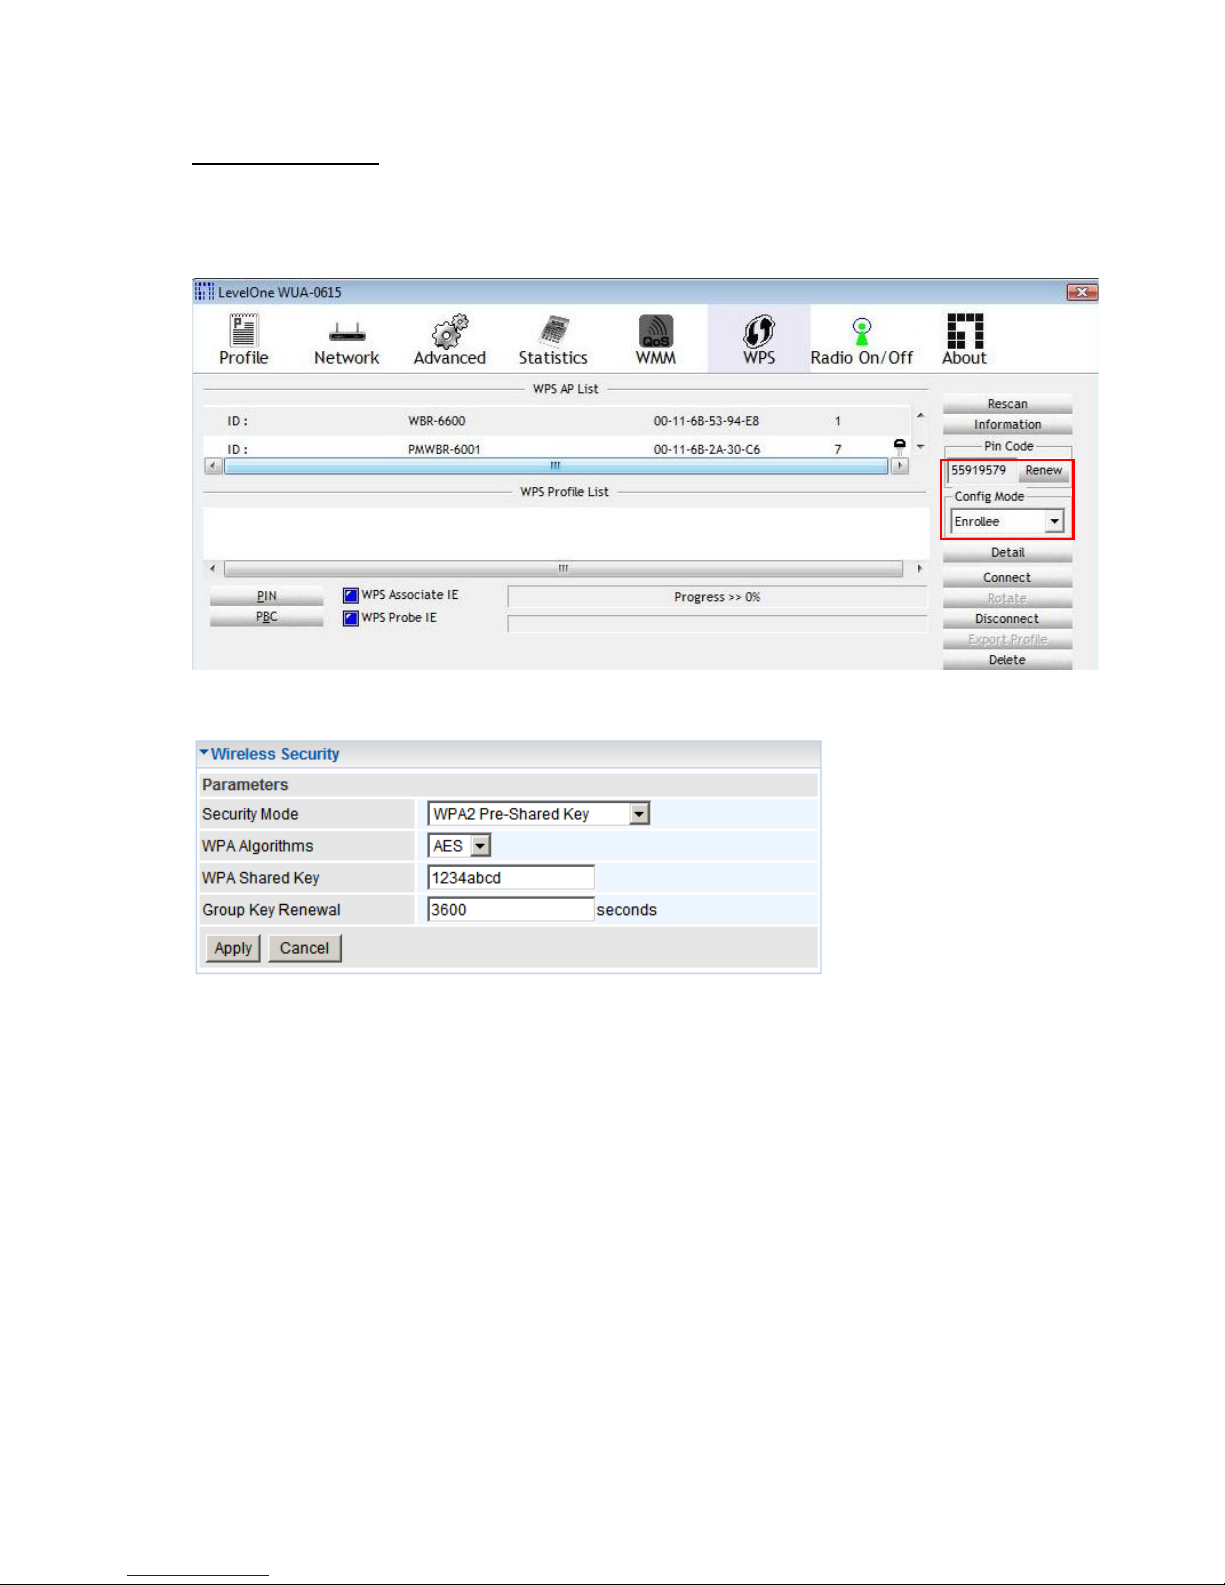
1. First, select the Enrollee mode and note down the WPS Pin code on your wireless
client‟s utility (Ex: 5919579).
2. Then proceed to set up your wireless security on the WBR-6600
Page 71
71
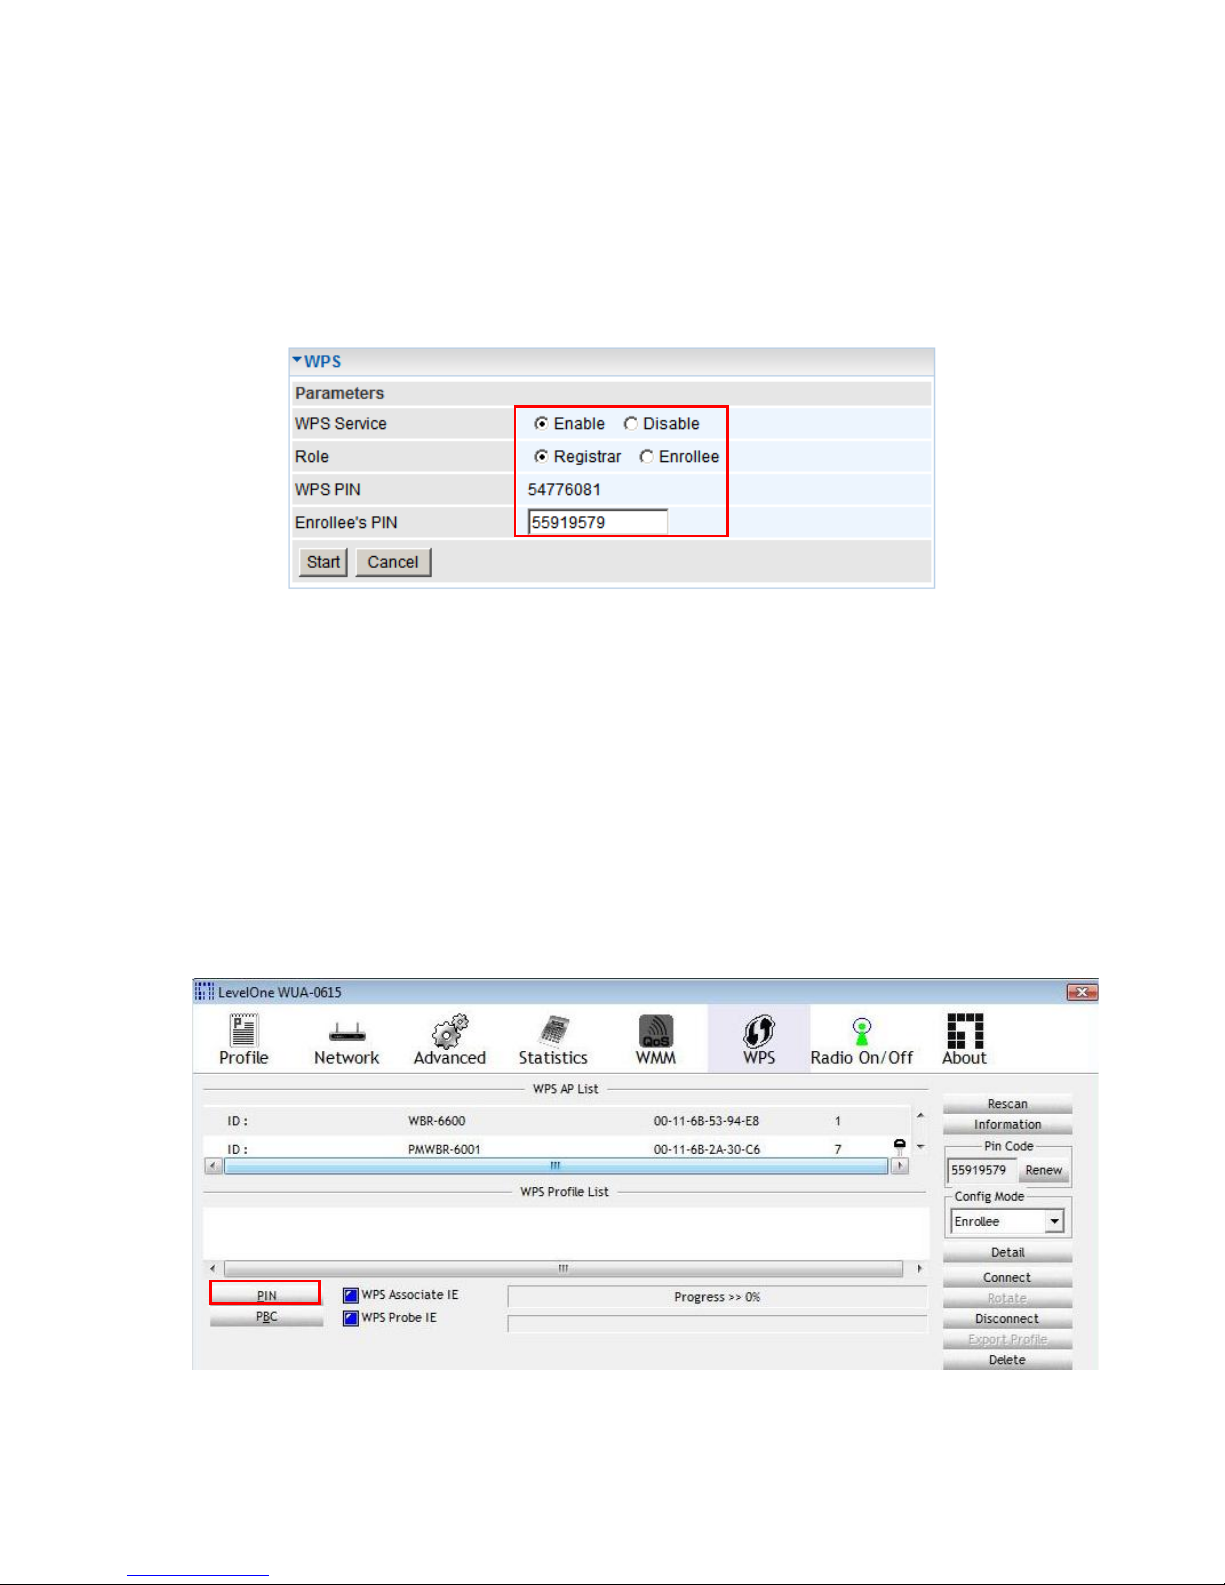
3. In the WBR-6600‟s WPS configuration page
a. Enable the WPS Service
b. Change Role to Registrar
c. Enter in the PIN Code on your wireless client
d. Click the Start button.
4. The router will now be waiting for other WPS devices to connect, as indicated by the
blinking WPS light.
In the future, you can set the router to search for WPS devices by pushing the
WBR-6600‟s WPS button on the back of the unit for 1 second and then release.
Note: The router will only wait 2 minutes for a client to connect. If you
take longer than 2 minutes to set up the client, then you will need to
re-initiate WPS on the WBR-6600.
5. Now click the PIN Code Method button on the wireless client‟s utility.
6. The wireless client should now have implemented the security settings on the
WBR-6600 and successfully achieved a connection.
Page 72
72
Set up WBR-6600 as WPS Enrollee
Using the Enrollee mode, it allows you to configure the network security settings from the
wireless client. Security parameters such as SSID and Passphrases could be randomly
generated, or set manually.
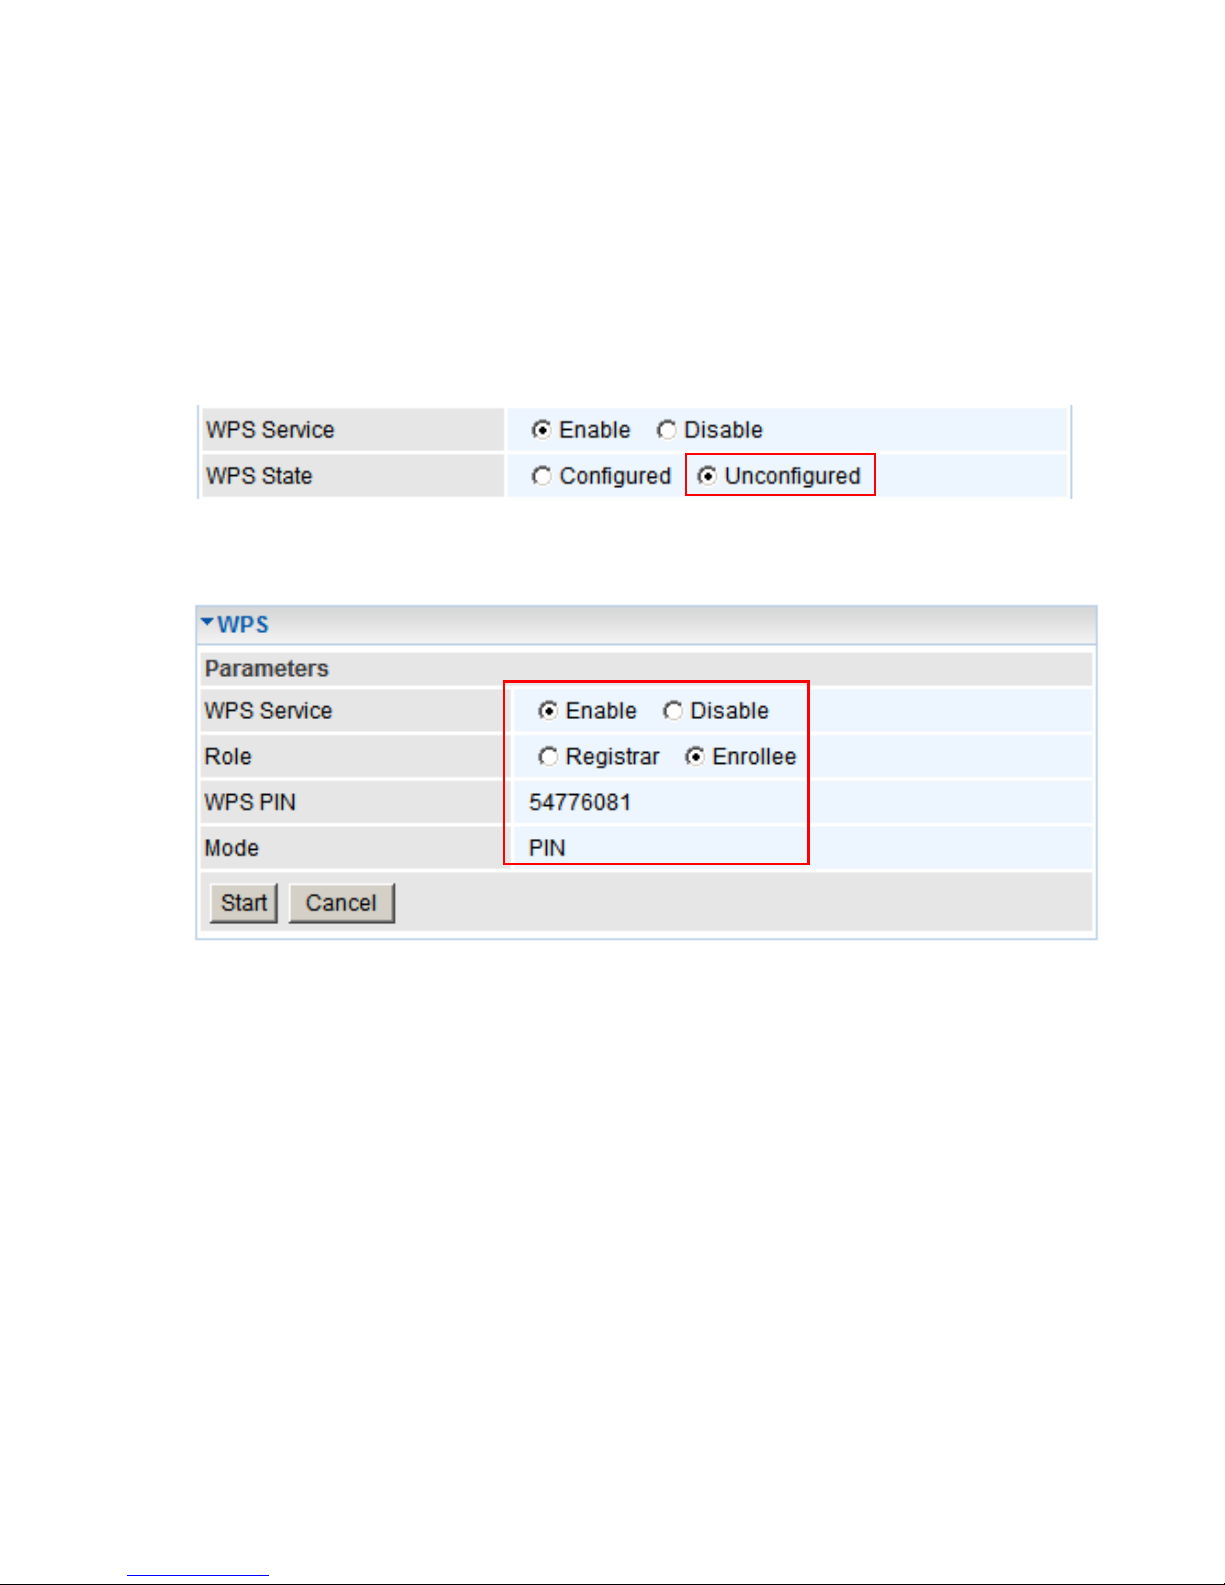
1. Ensure that the WPS is Enabled on the WBR-6600 and the Mode is set to
Unconfigured.
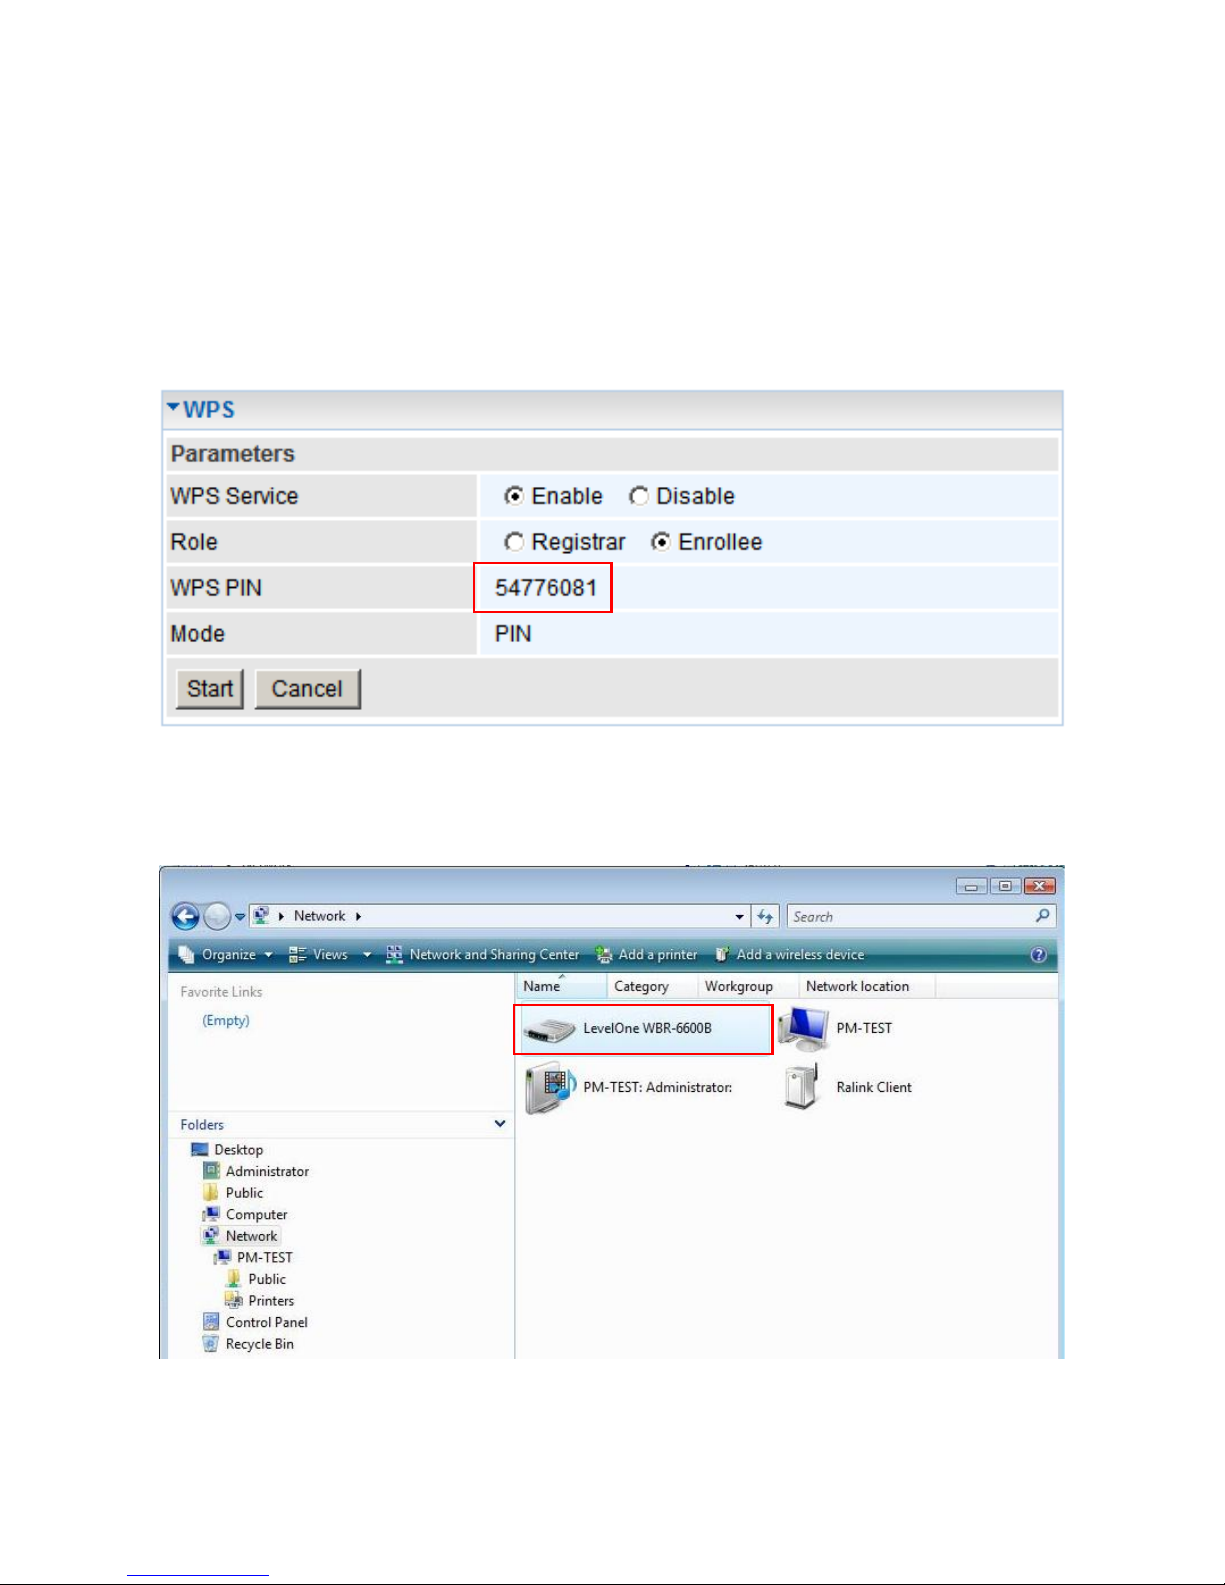
2. In the WPS Settings, set the role to Enrollee, note down the WPS Pin number of the
WBR-6600, then press Start.
Page 73
73
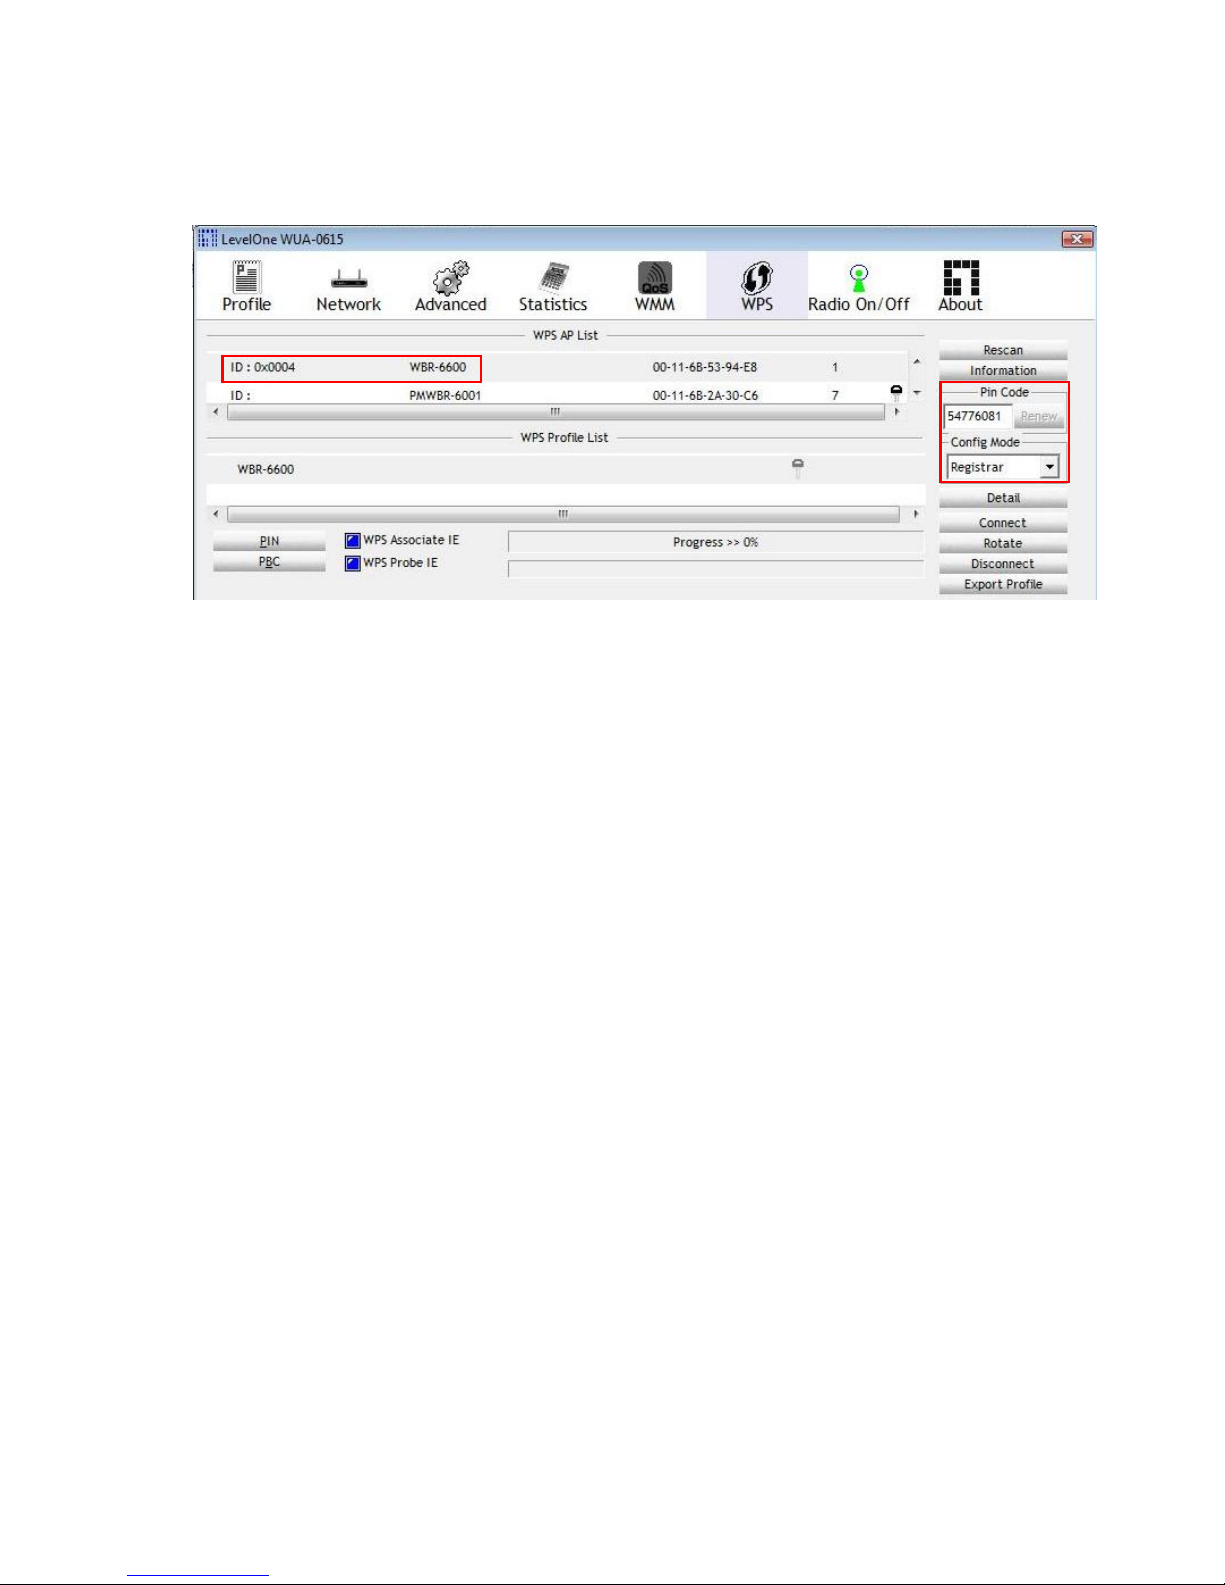
3. Once the WBR-6600 has initiated WPS function, it will be listed in the AP List of the
wireless client‟s utility.
4. Set the client to Registrar mode and enter the PIN number of the WBR-6600.
5. Click PIN to begin WPS pairing.
Note: Some utilities may set the security settings for you using randomly generated keys.
Some others may prompt you to enter the ones you want.
Page 74
74
Set up WBR-6600 using WPS with Vista
Note: Before beginning, please ensure that you have a wired connection to the
WBR-6600.
1. Set up the WBR-6600 for WPS Enrollee. (page 68)
2. Remember to note down the WBR-6600‟s PIN Code.
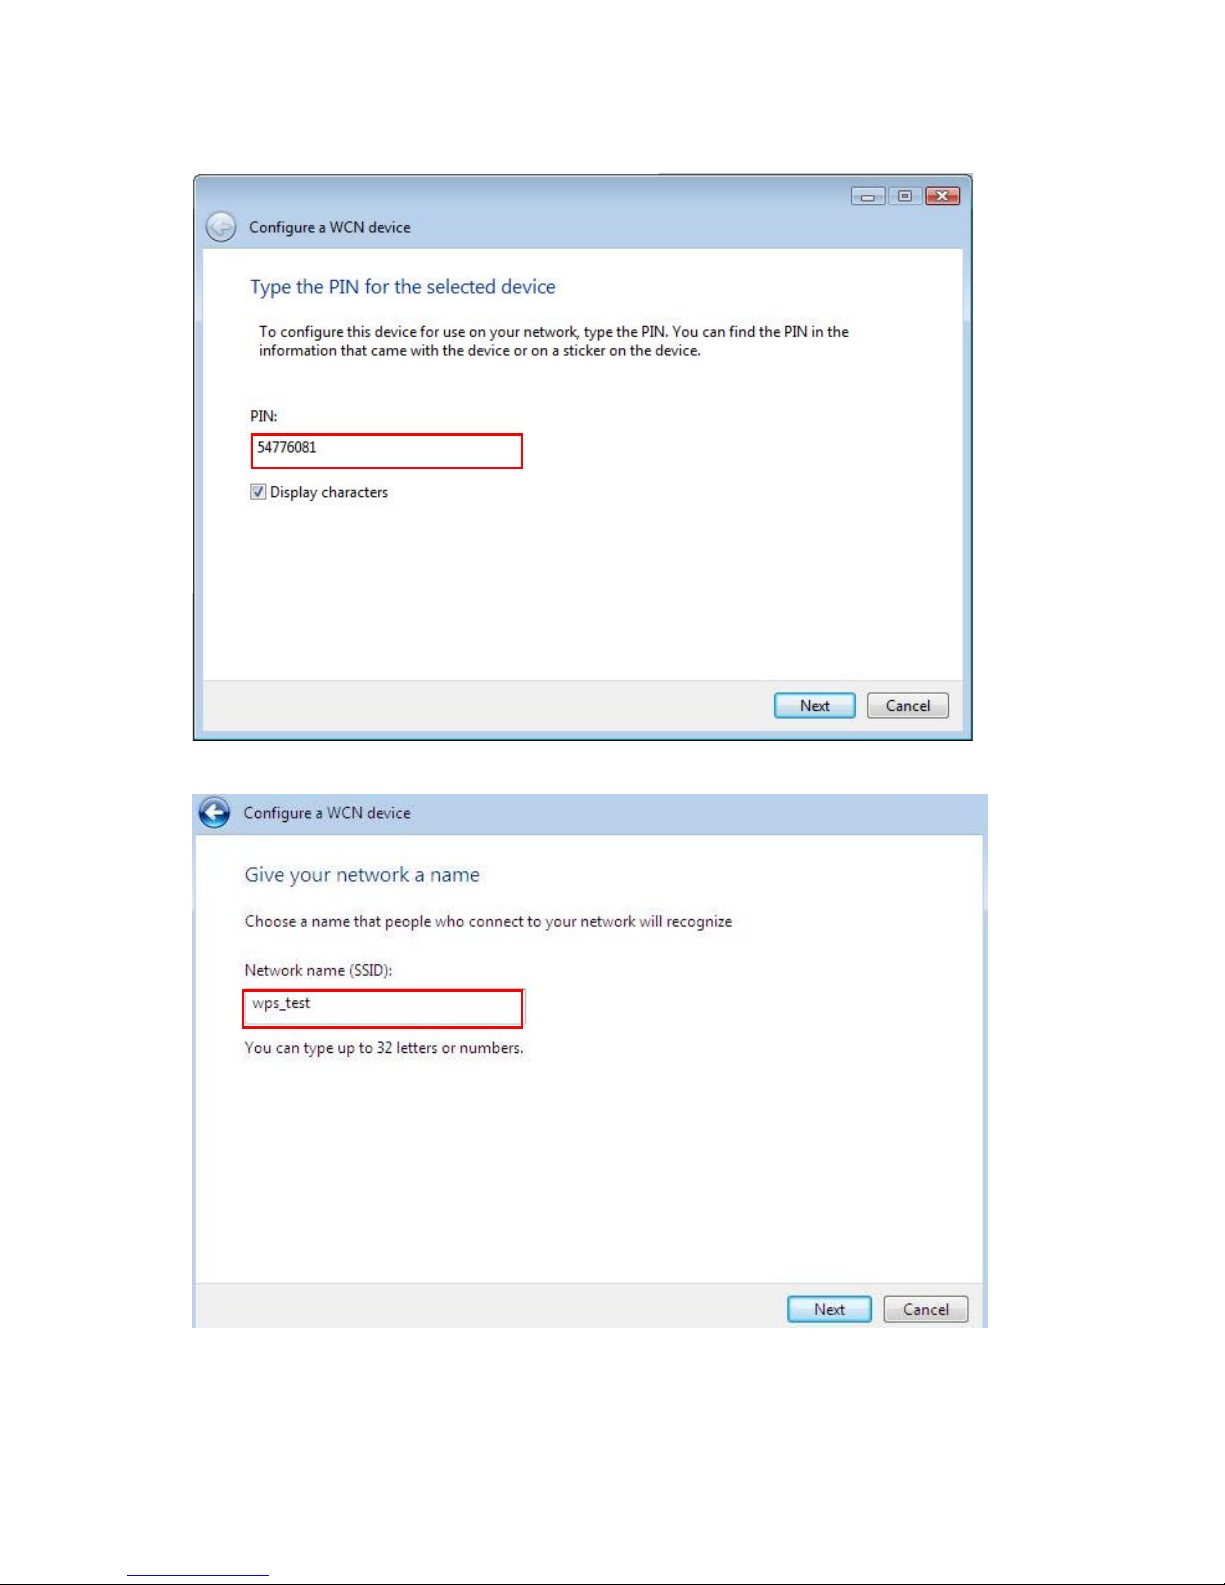
3. In Vista`s Control Panel, select Network and Internet and choose View network
computers and devices.
4. Double click the “LevelOne WBR-6600” icon
Page 75
75
5. Enter the WBR-6600‟s PIN Code and click Next.
6. Enter the Wireless Network Name (SSID) you want and click the “Next” button.
Page 76
76
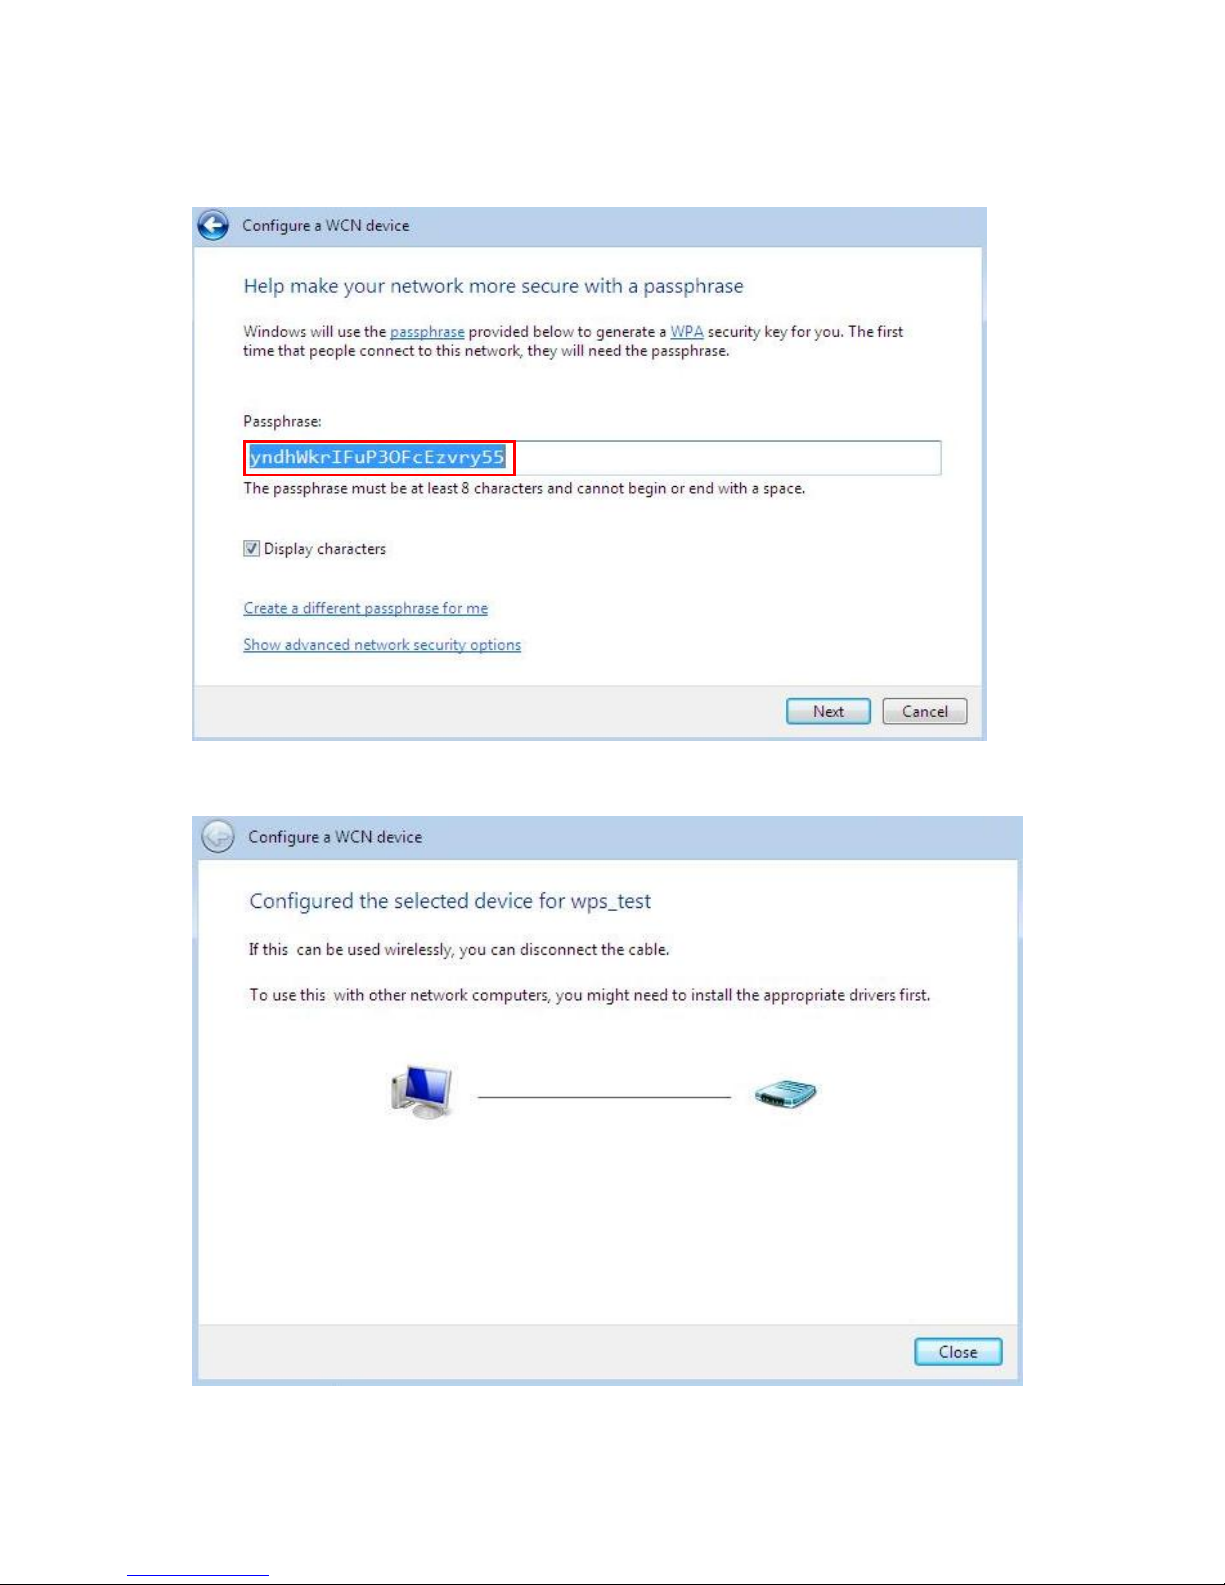
7. Enter the Passphrase and apply “Next” button.
(You can use the one Vista randomly creates, or type your own)
8. WCN set up complete. You have set up a security-enabled Wi-Fi network.
Page 77
77
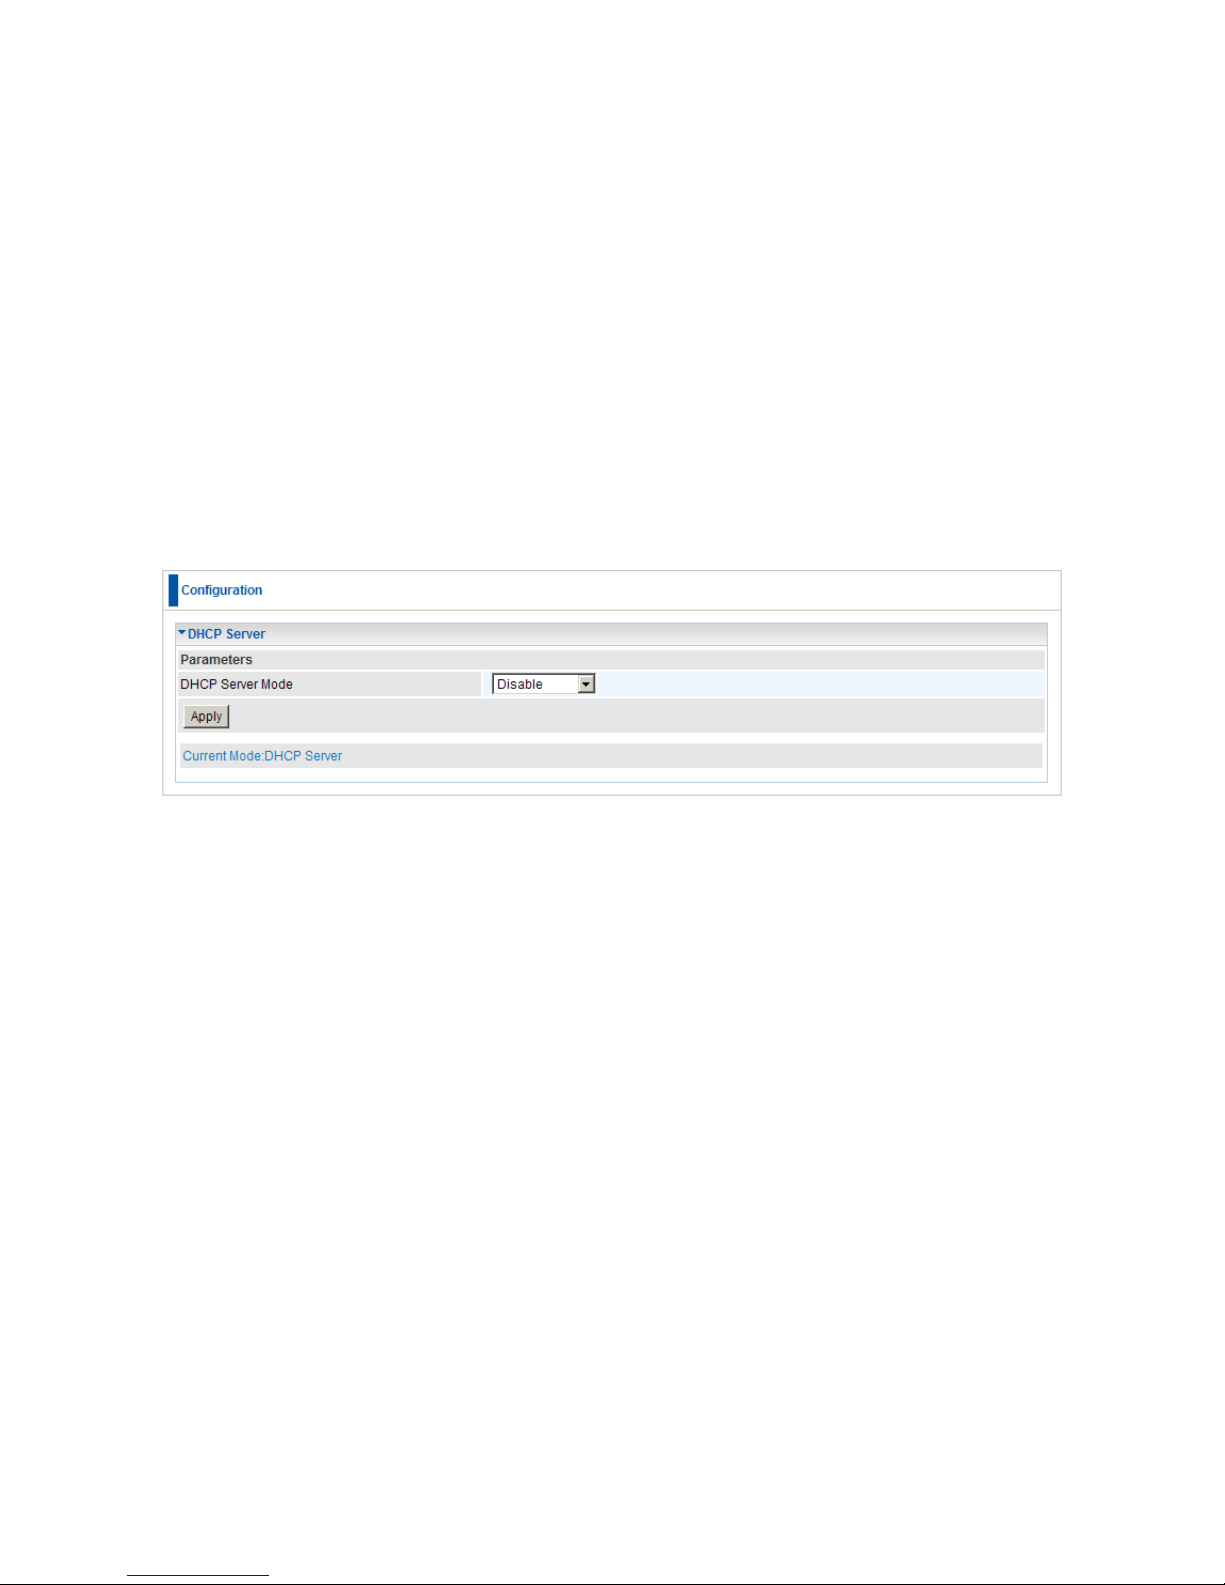
DHCP Server
You can disable or enable the DHCP (Dynamic Host Configuration Protocol) server or
enable the router‟s DHCP relay functions. The DHCP protocol allows your router to
dynamically assign IP addresses to PCs on your network if they are configured to obtain
IP addresses automatically.
DHCP Server Mode: Disable
To disable the router‟s DHCP Server, check Disabled and then click Apply. When the
DHCP Server is disabled, you will need to manually assign a fixed IP address to each PC
on your network, and set the default gateway for each PC to the IP address of the router
(the default is 192.168.0.1).
Page 78
78
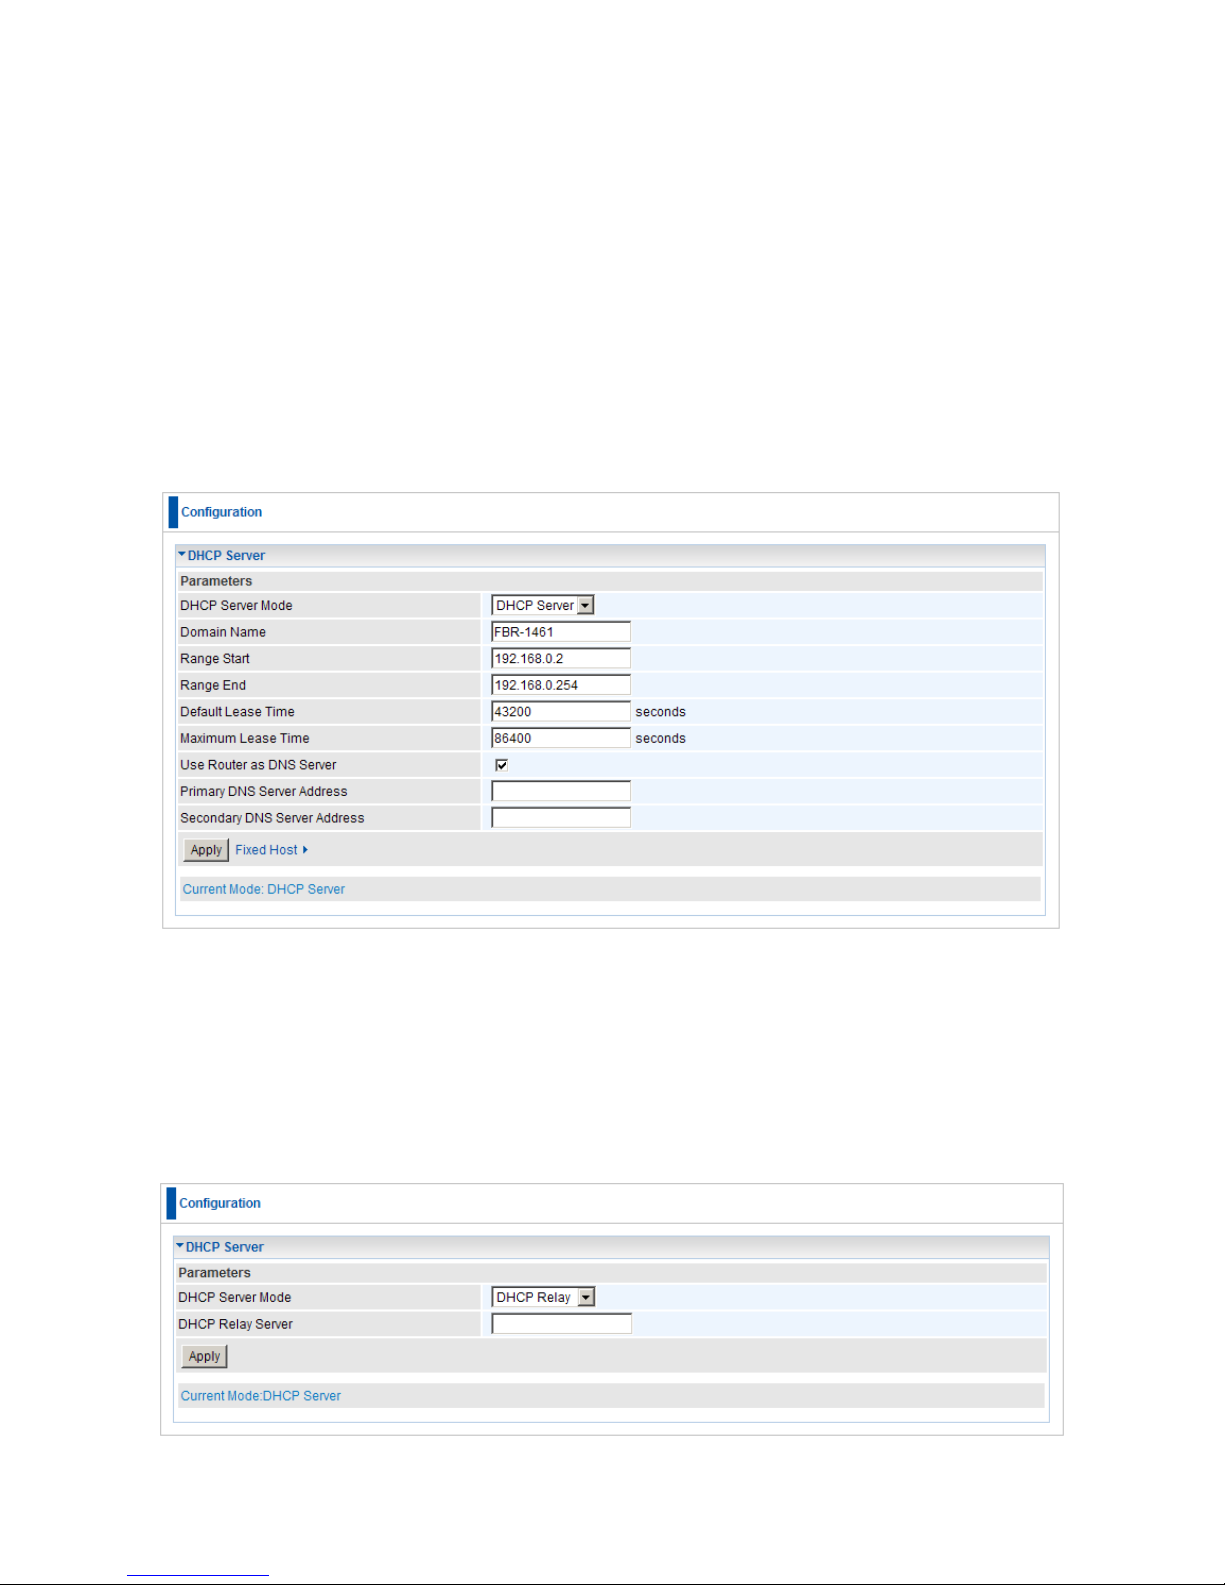
DHCP Server Mode: DHCP Server
To configure the router‟s DHCP Server, check DHCP Server. You can then configure
parameters of the DHCP Server including the IP pool (starting IP address and ending IP
address to be allocated to PCs on your network), lease time for each assigned IP
address (the period of time the IP address assigned will be valid), DNS IP address and
the gateway IP address. These details are sent to the DHCP client (i.e. your PC) when it
requests an IP address from the DHCP server. Click Apply to enable this function. If you
check “Use Router as a DNS Server”, the ADSL Router performs the domain name
lookup, finds the IP address from the outside network automatically and forwards it back
to the requesting PC in the LAN (your Local Area Network).
DHCP Server Mode: DHCP Relay
If you check DHCP Relay and then you must enter the IP address of the DHCP server
which assigns an IP address back to the DHCP client in the LAN. Use this function only if
advised to do so by your network administrator or ISP. Click Apply to enable this function.
This feature is only where the DHCP server is on the WAN.
Page 79
79
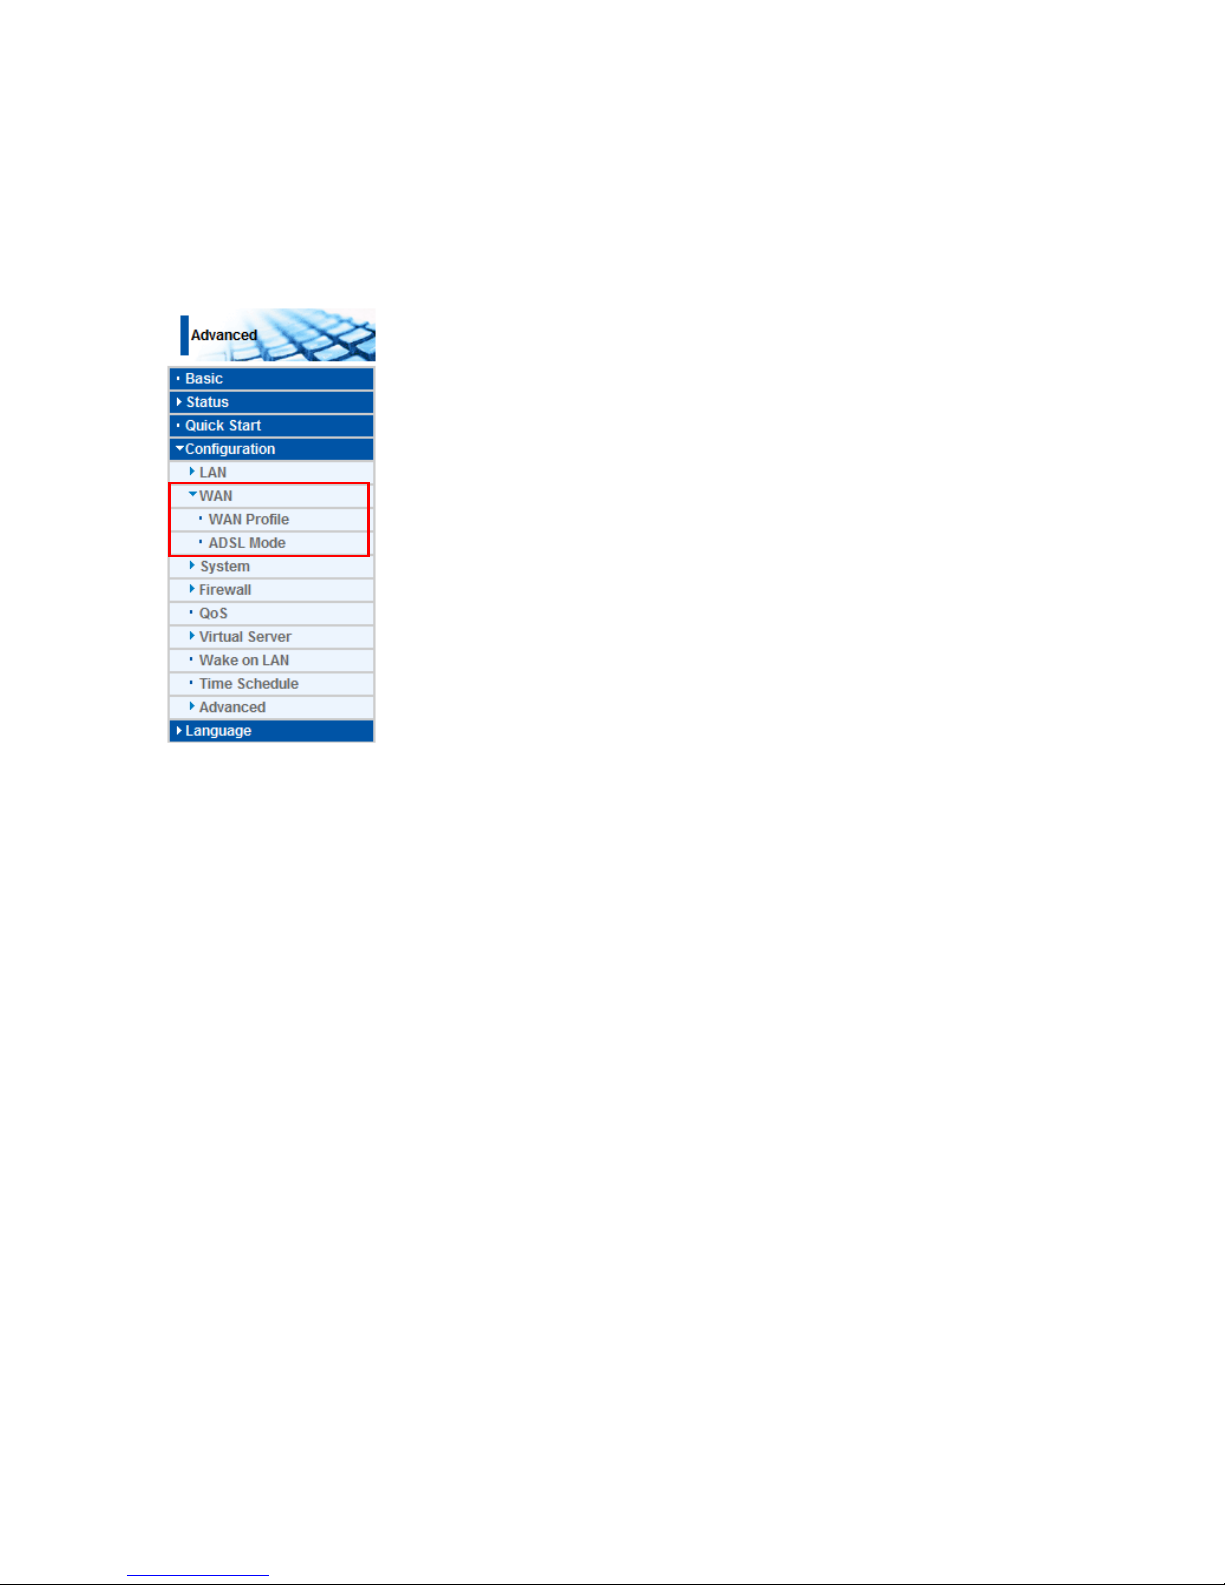
WAN (Wide Area Network)
A WAN (Wide Area Network) is an outside connection to another network or the Internet.
There are two items within the WAN section: WAN Profile and ADSL Mode.
Page 80
80
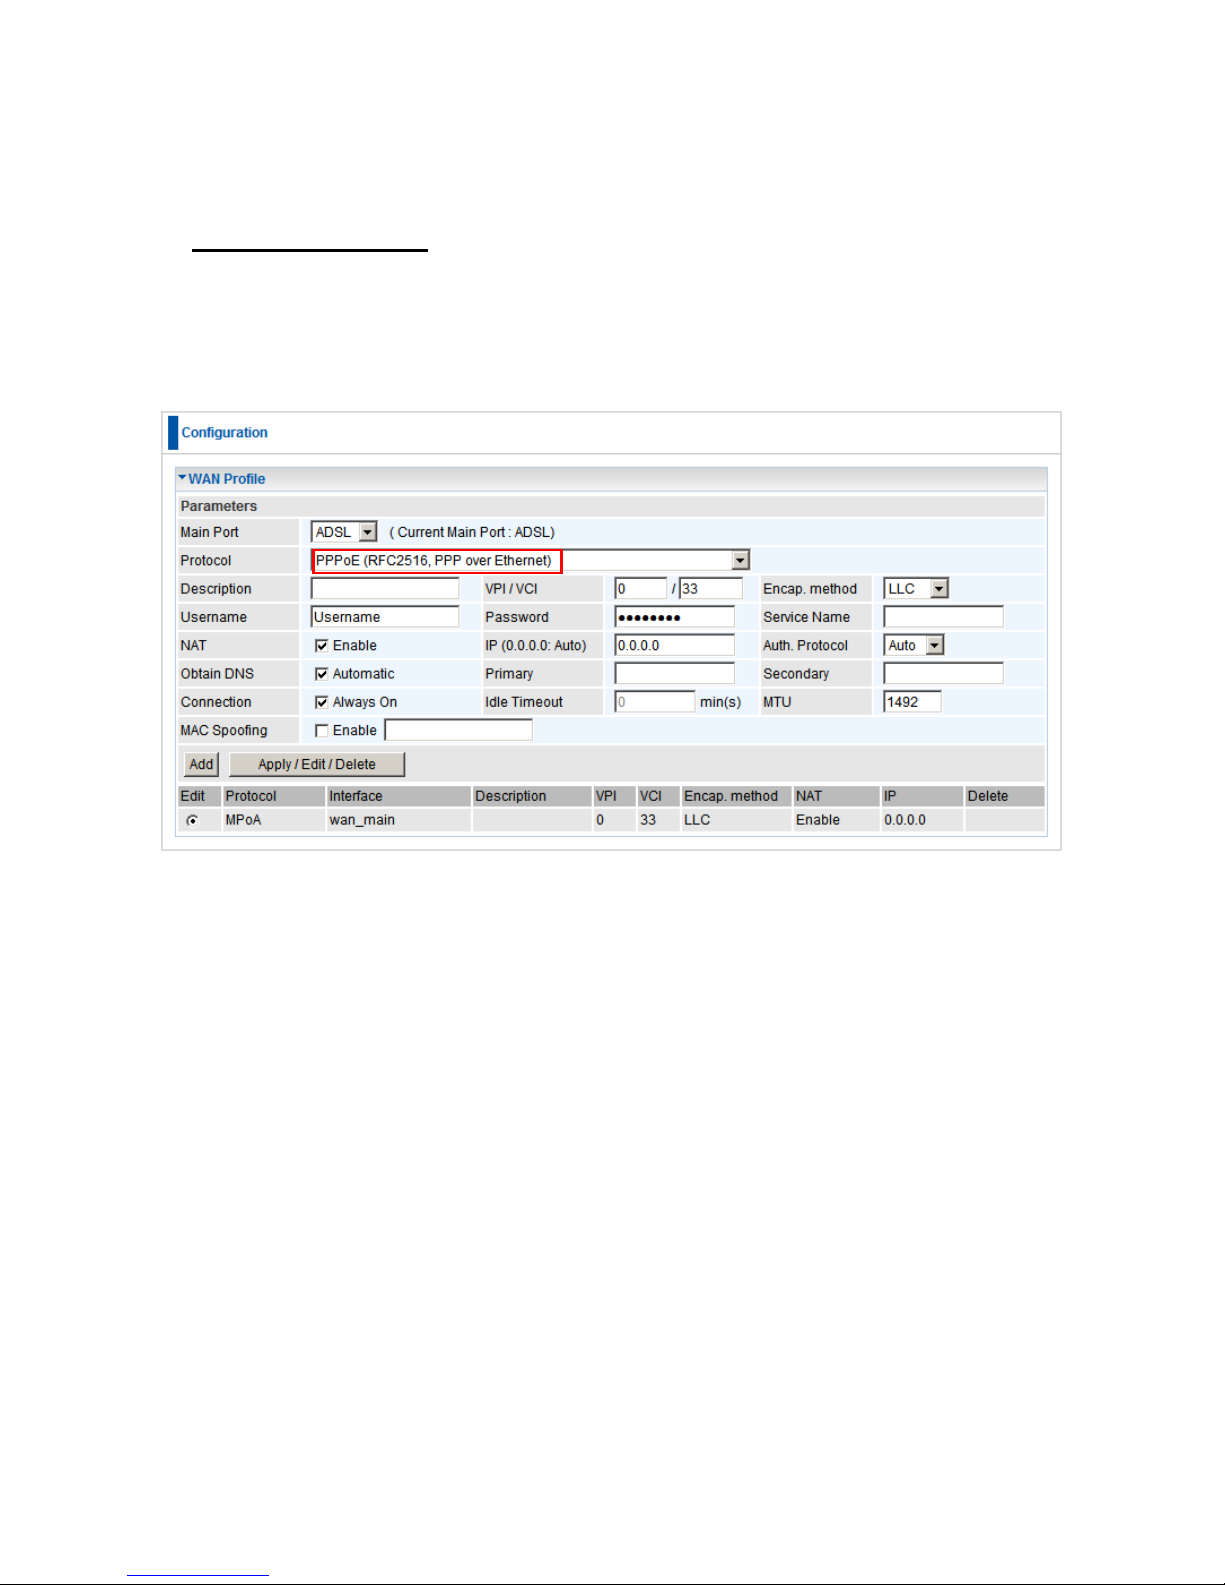
WAN Profile
Profile Port - ADSL
PPPoE Connection
PPPoE (PPP over Ethernet) provides access control in a manner similar to dial-up
services using PPP.
Description: A user-definable name for this connection.
VPI/VCI: Enter the VPI and VCI information provided by your ISP.
Encap. method: Select the encapsulation format, the default is LLC. Select the one
provided by your ISP
Username: Enter the username provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive). This is in the format of
“username@ispname” instead of simply “username”.
Password: Enter the password provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive)
Service Name: This item is for identification purposes. If it is required, your ISP
provides you the information. Maximum input is 15 alphanumeric characters.
NAT: The NAT (Network Address Translation) feature allows multiple users to access
the Internet through a single ISP account, sharing a single IP address. If users on your
LAN have public IP addresses and can access the Internet directly, the NAT function
can be disabled.
Page 81
81
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Auth. Protocol: Default is Auto. Your ISP advises on using Chap or Pap.
Obtain DNS Automatically: Select this check box to use DNS.
Primary DNS/ Secondary DNS: Enter the IP addresses of the DNS servers. The DNS
servers are passed to the DHCP clients along with the IP address and the subnet
mask.
Connection:
Always on: If you want the router to establish a PPPoE session when starting
up and to automatically re-establish the PPPoE session when disconnected
by the ISP.
Connect to Demand (un-select Always On): If you want to establish a
PPPoE session only when there is a packet requesting access to the Internet
(i.e. when a program on your computer attempts to access the Internet). In
this mode, you must set Idle Timeout value at same time.
Idle Timeout: Auto-disconnect the broadband firewall gateway when there is no
activity on the line for a predetermined period of time. The minimum value is 10
minutes.
MTU: Maximum Transmission Unit. The size of the largest datagram (excluding
media-specific headers) an IP attempts to send through the interface.
Page 82
82
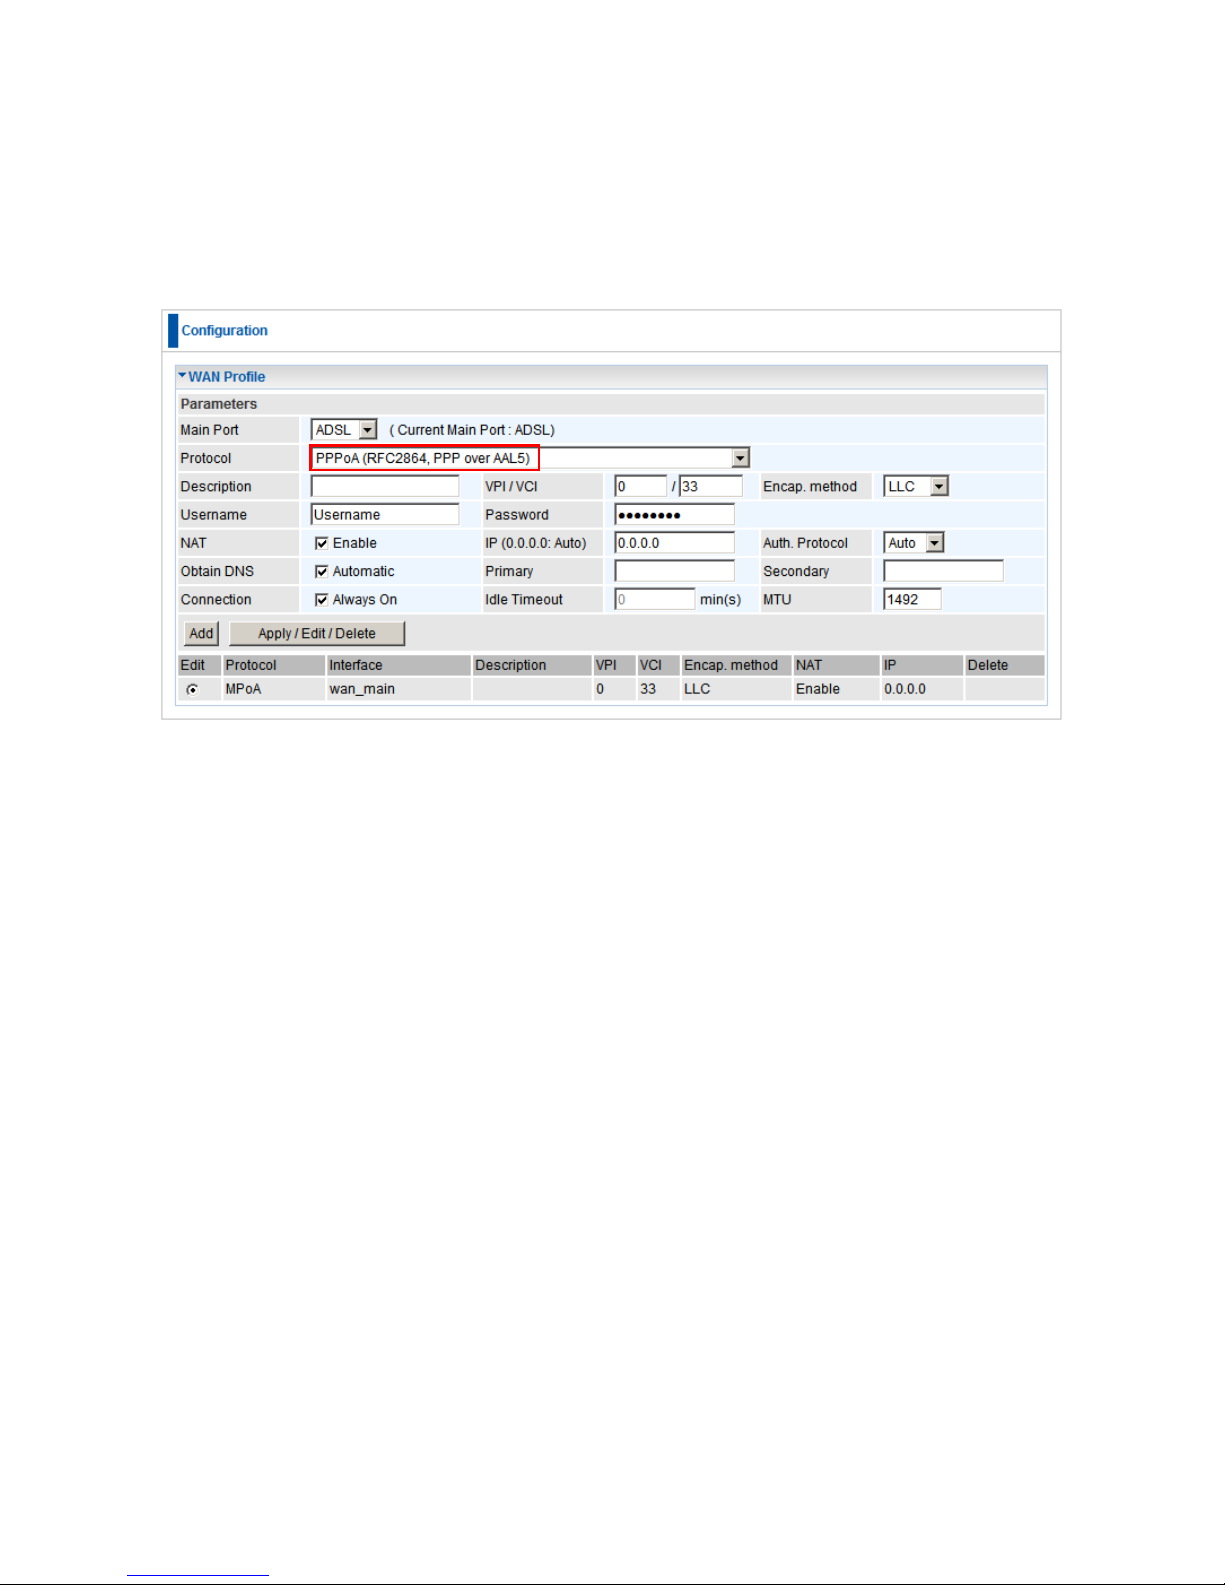
PPPoA Connection
PPPoA stands for Point to Point Protocol over ATM Adaptation Layer 5 (AAL5). It
provides access control and billing functionality in a manner similar to dial-up services
using PPP.
Description: User-definable name for the connection.
VPI/VCI: Enter the VPI and VCI information provided by your ISP.
Encapsulation method: Select the encapsulation format, the default is LLC. Select
the one provided by your ISP
Username: Enter the username provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive). This is in the format of
“username@ispname” instead of simply “username”.
Password: Enter the password provided by your ISP. You can input up to 128
alphanumeric characters (case sensitive).
NAT: The NAT (Network Address Translation) feature allows multiple users to access
the Internet through a single IP account, sharing a single IP address. If users on your
LAN have public IP addresses and can access the Internet directly, the NAT function
can be disabled.
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Authentication Protocol: Default is Auto. Your ISP should advises you on whether to
use Chap or Pap.
Obtain DNS Automatically: Select this check box to use DNS.
Page 83
83
Primary DNS/ Secondary DNS: Enter the IP addresses of the DNS servers. The DNS
servers are passed to the DHCP clients along with the IP address and the subnet
mask.
Connection:
Always on: The router will establish a PPPoA session when starting up and to
automatically re-establish the PPPoA session when disconnected by the ISP.
Connect to Demand (un-select Always On): If you want to establish a
PPPoA session only when there is a packet requesting access to the Internet
(i.e. when a program on your computer attempts to access the Internet). In
this mode, you must set Idle Timeout value at same time.
Idle Timeout: Auto-disconnect the broadband firewall gateway when there is no
activity on the line for a predetermined period of time. The minimum value is 10
minutes.
MTU: Maximum Transmission Unit. The size of the largest datagram (excluding
media-specific headers) that the IP attempts to send through the interface.
Page 84
84
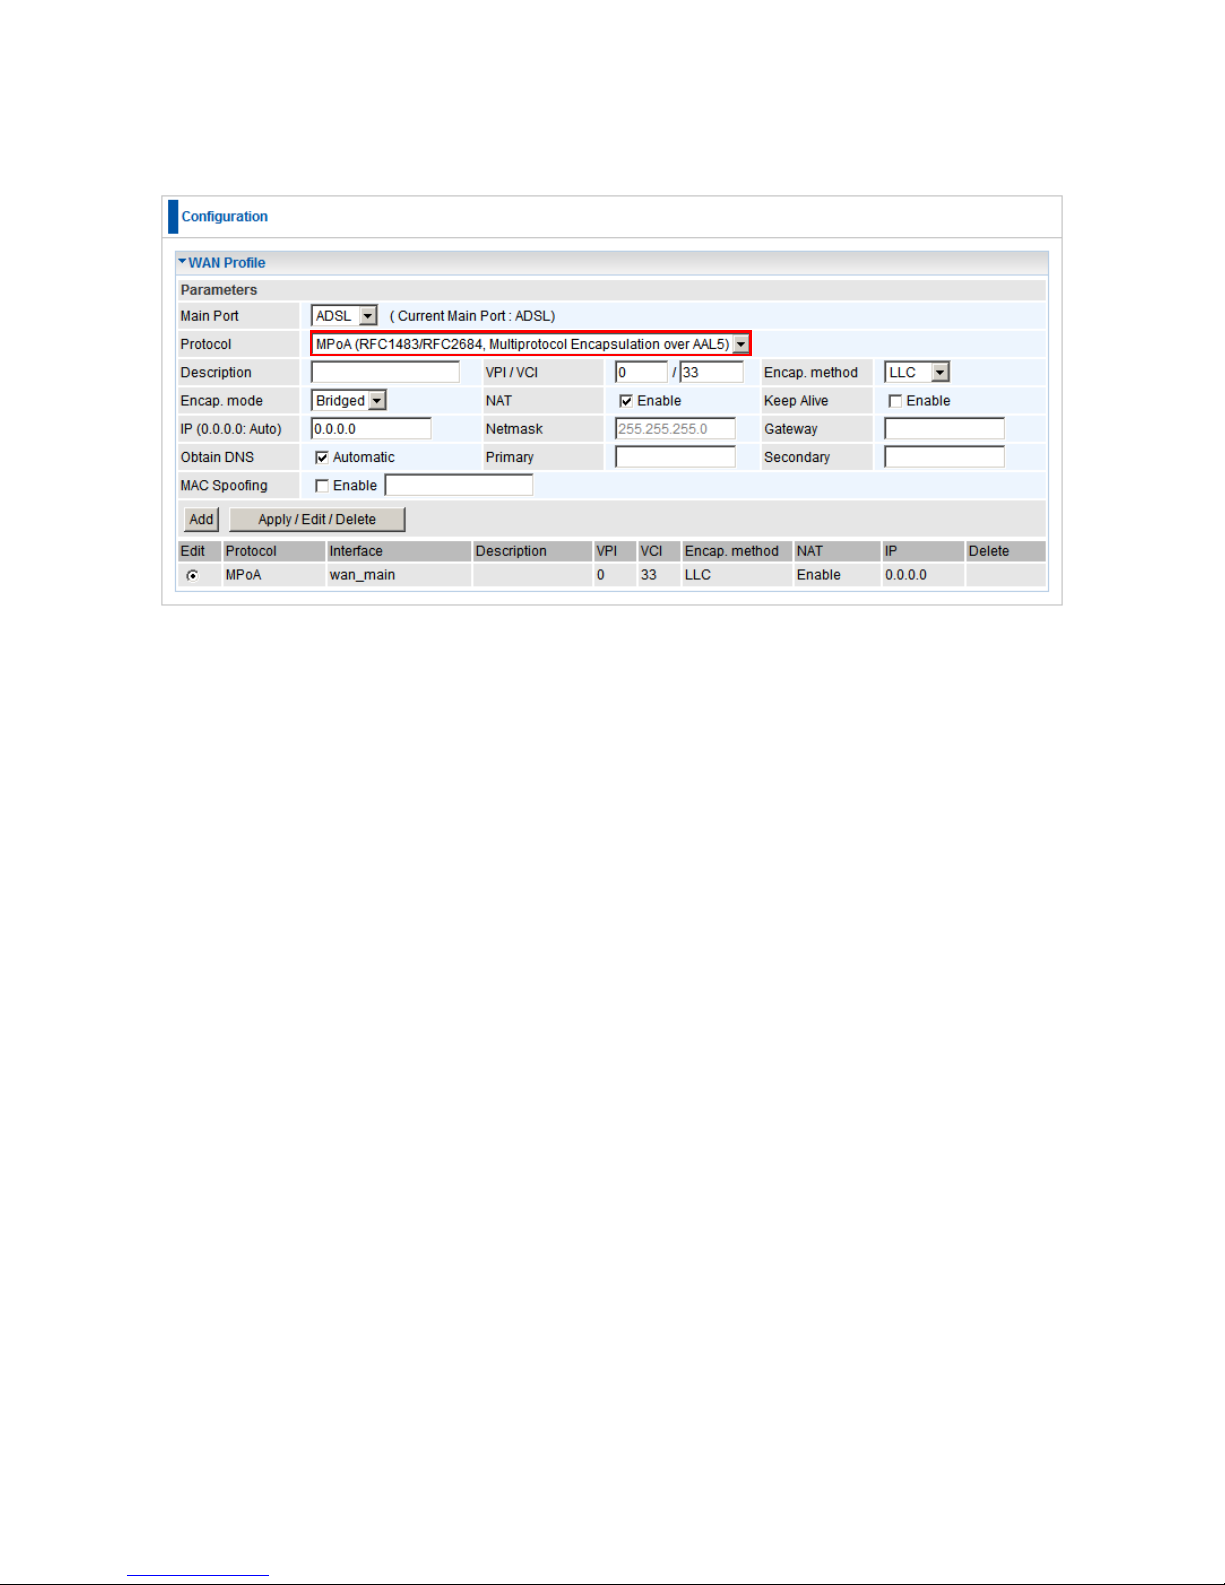
MPoA Connection
Description: Your description of this connection.
VPI and VCI: Enter the VPI and VCI information provided by your ISP.
Encap. method: Select the encapsulation format, the default is LLC. Select the one
provided by your ISP.
Encap. mode: Choose whether you want the device to function as bridge mode or
routing mode.
NAT: The NAT (Network Address Translation) feature allows multiple users to access
the Internet through a single IP account, sharing the single IP address. If users on your
LAN have public IP addresses and can access the Internet directly, the NAT function
can be disabled.
IP Address: Your WAN IP address. Leave this at 0.0.0.0 to automatically obtain an IP
address from your ISP.
Netmask: The default is 255.255.255.0. User can change it to other such as
255.255.255.128. Type the subnet mask assigned to you by your ISP (if given)
Gateway: Enter the IP address of the default gateway.
Obtain DNS Automatically: Select this check box to use DNS.
Primary DNS/ Secondary DNS: Enter the IP addresses of the DNS servers. The DNS
servers are passed to the DHCP clients along with the IP address and the subnet
mask.
Page 85
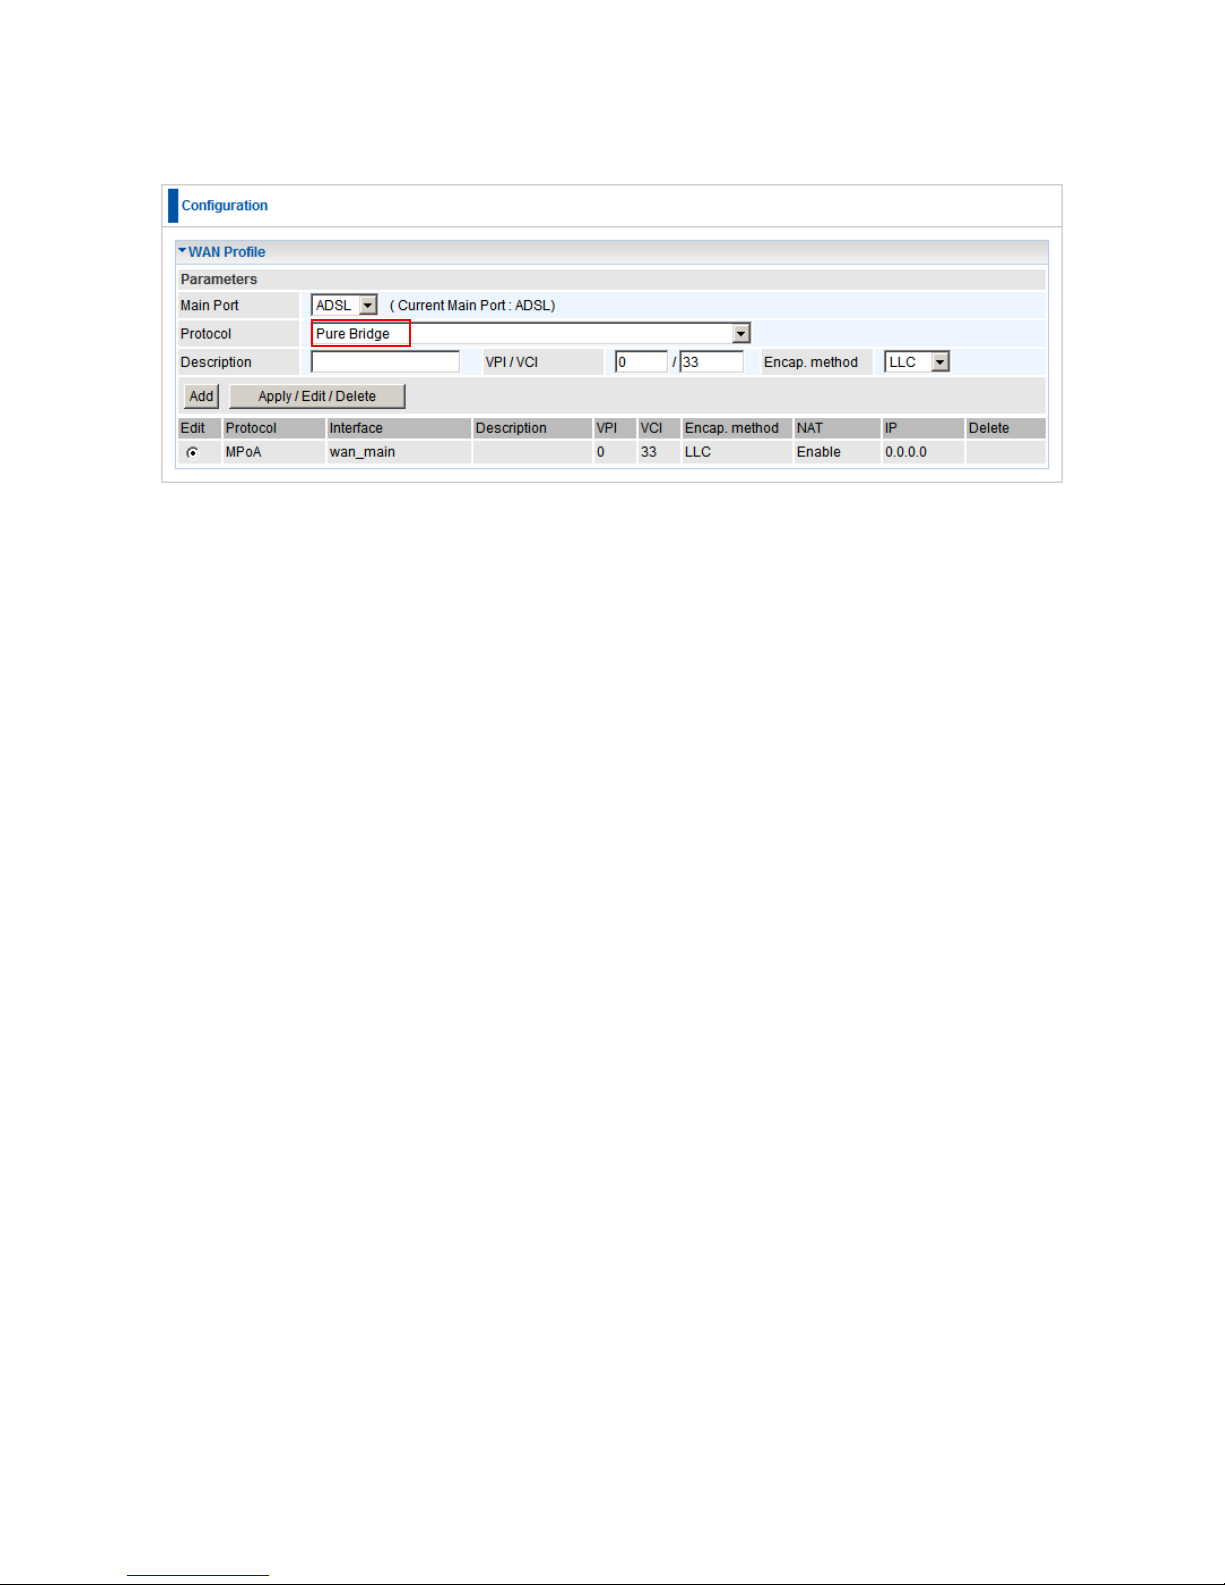
85
Pure Bridge Connections
Description: A user-definable name for this connection.
VPI/VCI: Enter the VPI and VCI information provided by your ISP.
Encap. method: Select the encapsulation format, this is provided by your ISP.
Page 86
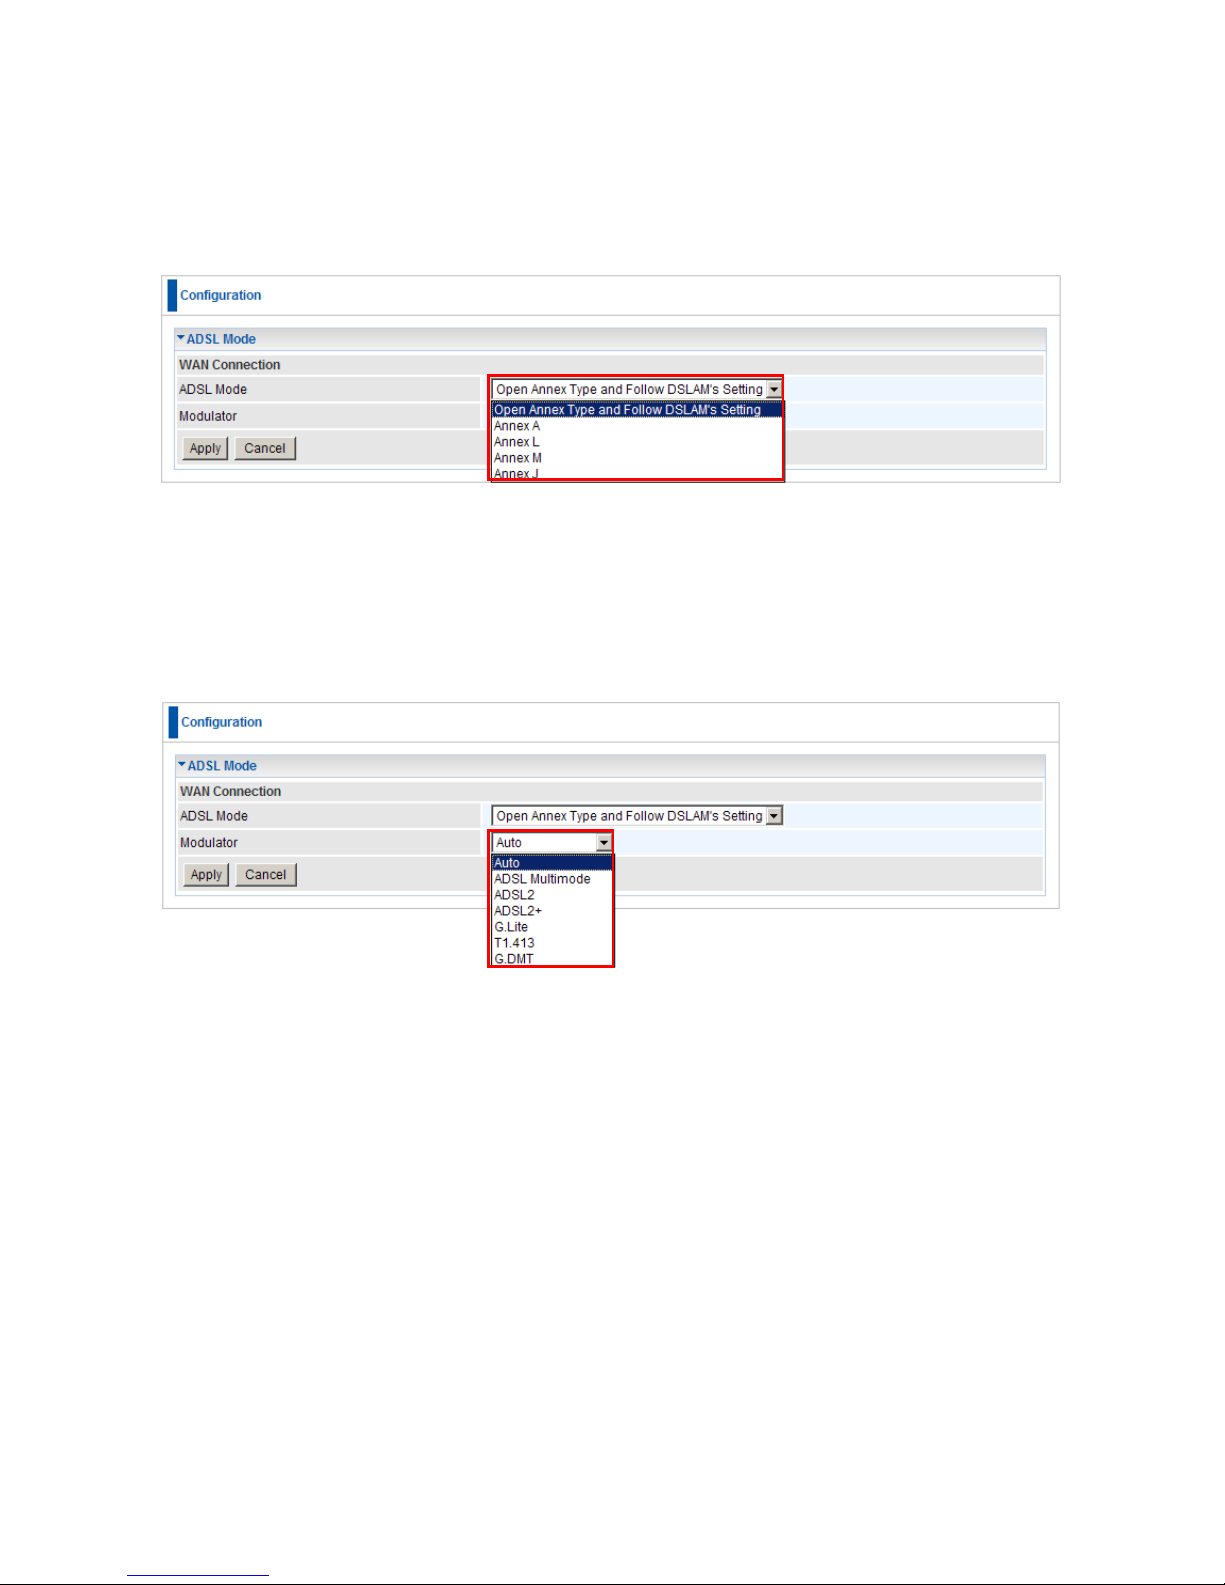
86
ADSL Mode
WBR-6600A (Annex A)
ADSL Mode: There are four modes “Open Annex Type and Follow DSLAM’s
Setting”, ”Annex A”, ”Annex L”, ”Annex M” and “Annex J” that user can select for this
connection.
Modulator: There are seven modes “AUTO”,”ADSL multimode”,”ADSL2”,”ADSL2+”,
“G.Lite:”, “T1.413” and “G.DMT” that user can select for this connection.
Page 87
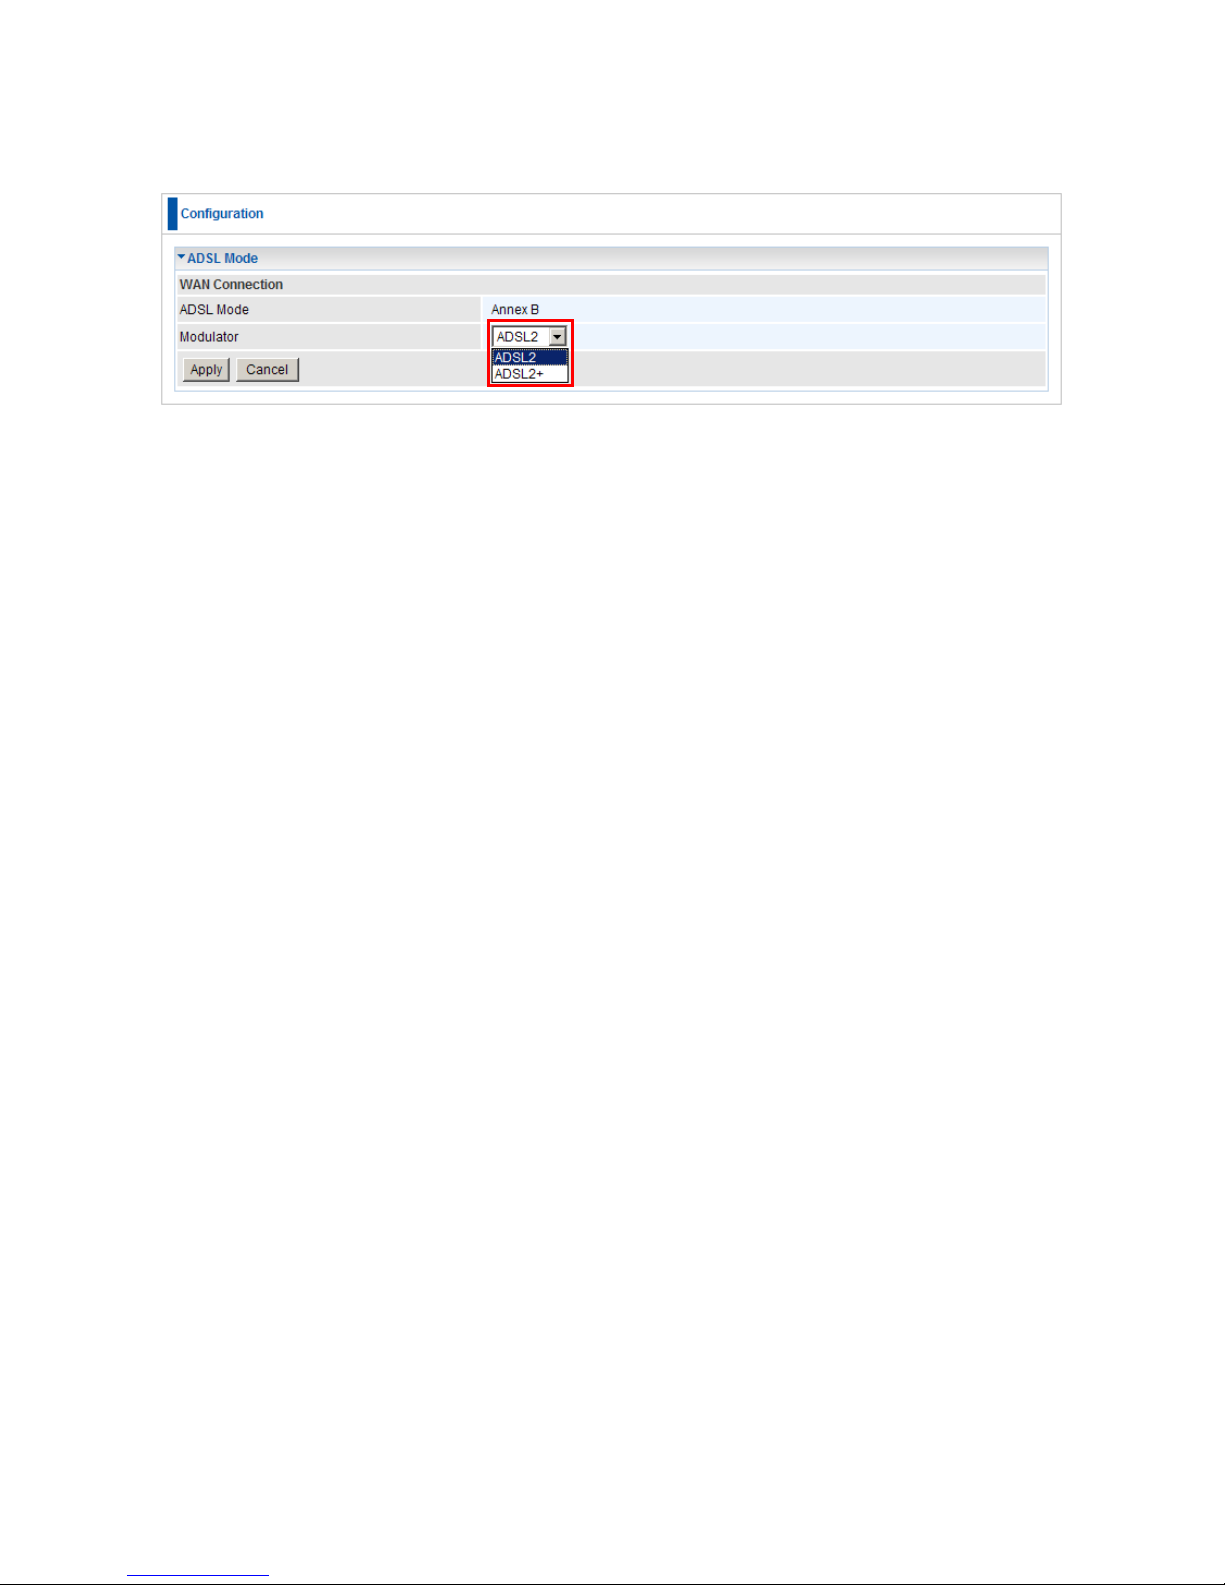
87
WBR-6600B (Annex B)
Modulator: There are two modes”ADSL2” and”ADSL2+” that user can select for this
connection.
Page 88
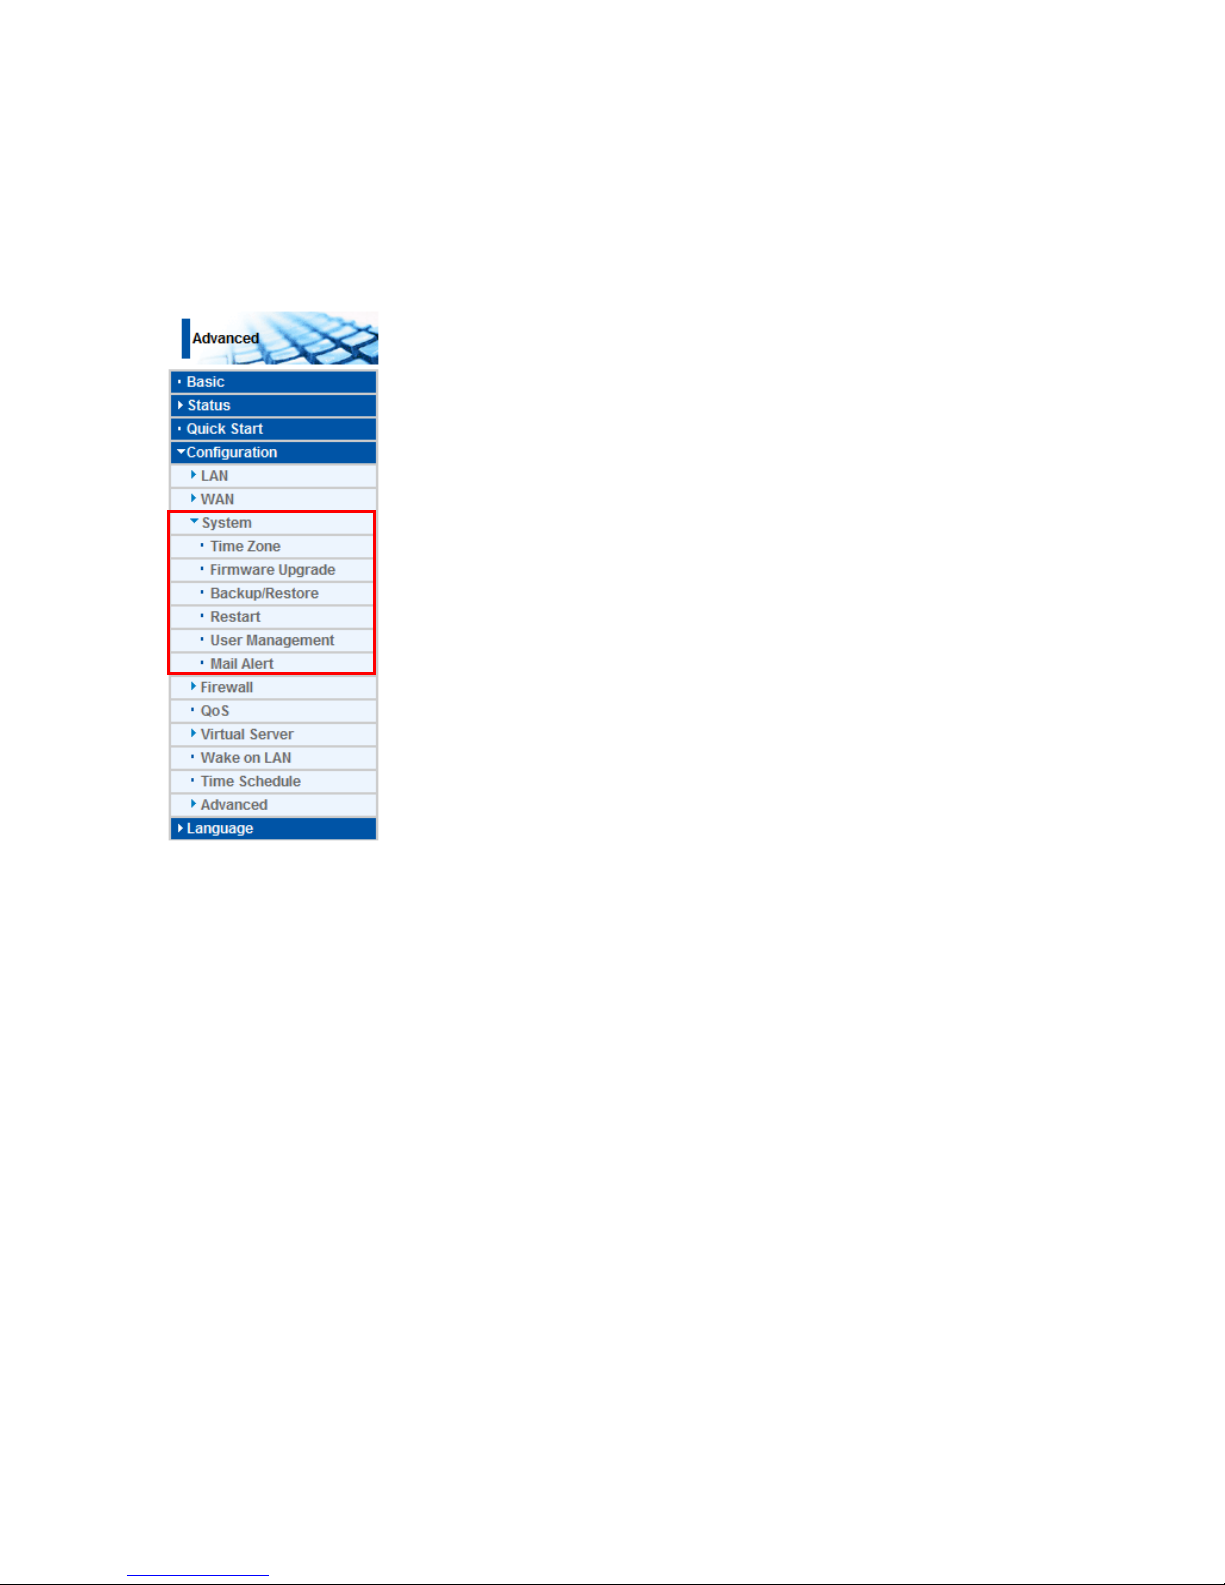
88
System
There are six items within the System section: Time Zone, Firmware Upgrade,
Backup/Restore, Restart, User Management and Mail Alert.
Page 89
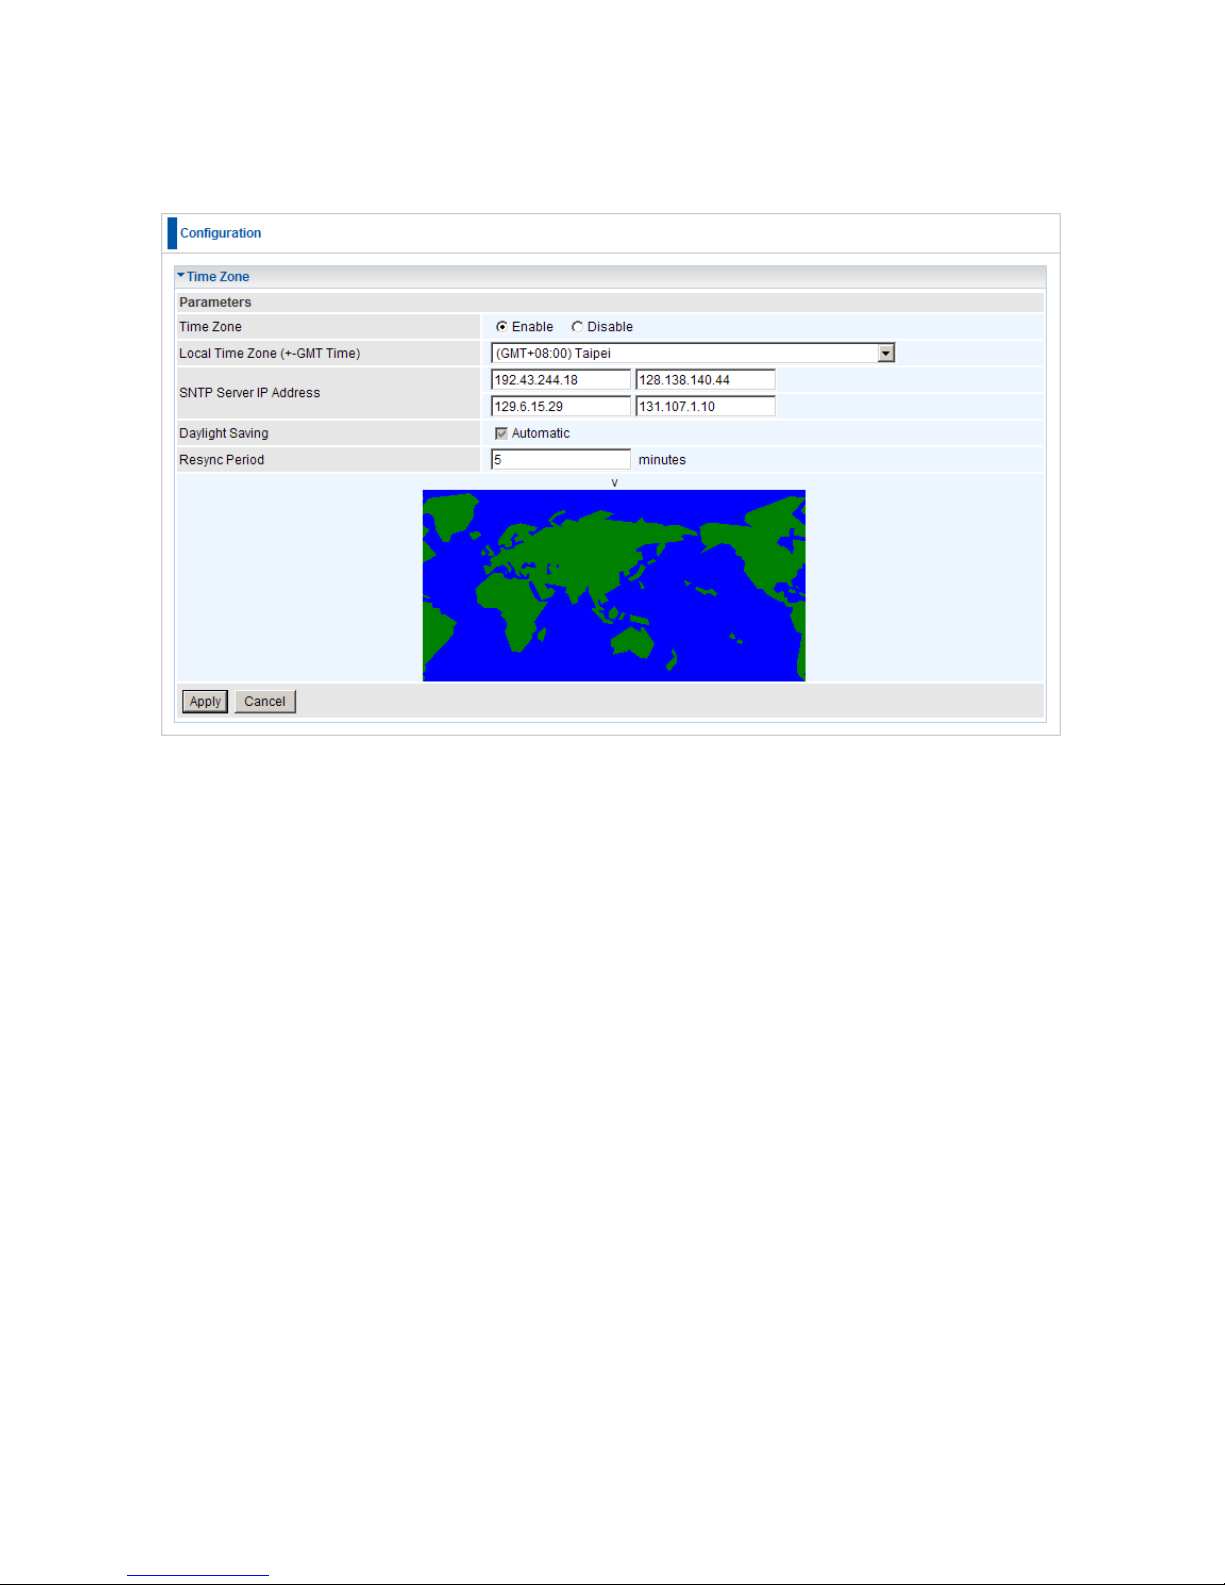
89
Time Zone
The router does not have a real time clock on board; instead, it uses the Simple Network
Time Protocol (SNTP) to get the current time from an SNTP server outside your network.
Choose your local time zone, click Enable and click the Apply button. After a successful
connection to the Internet, the router retrieves the correct local time from the SNTP server
you have specified. If you prefer to specify an SNTP server other than those in the
drop-down list, simply enter its IP address as shown above. Your ISP may provide an SNTP
server for you to use.
Resync Period (in minutes) is the periodic interval the router waits before it resynchronizes
the router‟s time with that of the specified SNTP server. To avoid unnecessarily increasing
the load on your specified SNTP server you should keep the poll interval as high as
possible – at the absolute minimum every few hours or even days.
Page 90
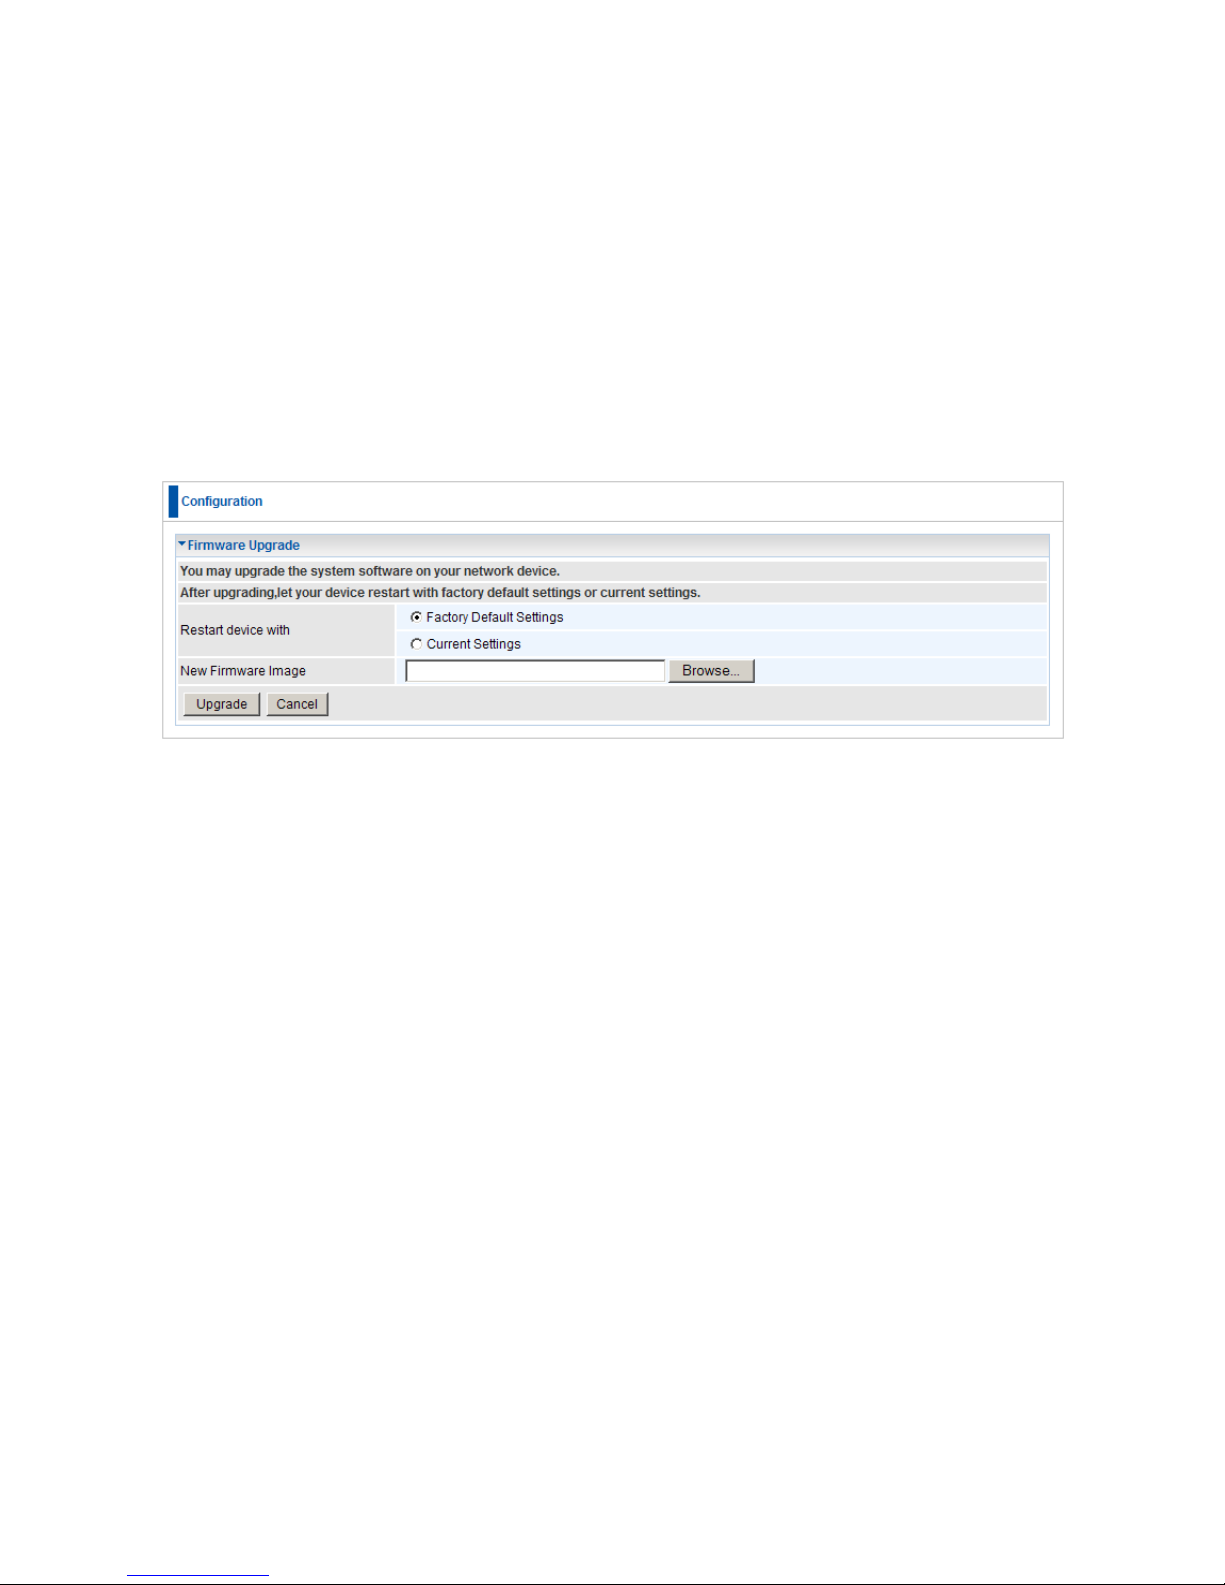
90
Firmware Upgrade
Your router‟s “firmware” is the software that allows it to operate and provides all its
functionality. Think of your router as a dedicated computer, and the firmware as the software
it runs. Over time this software may be improved and modified. Your router allows you to
upgrade the software it runs to take advantage of these changes.
Clicking on Browse allows you to select the new firmware image file you have downloaded
to your PC. Once the correct file is selected, click Upgrade to update the firmware in your
router.
Restart Device with: To choose “Factory Default Settings” or “Current Settings” which
uses your current setting on the new firmware (it is highly advised to use Factory Default
Settings over Current Settings for a clean firmware upgrade).
New Firmware Image: Type in the location of the file you wish to upload in this field or
click Browse… to locate it.
Browse…: Click Browse… to find the file with the .afw file extension that you wish to
upload. Remember that you must decompress compressed (.zip) files before you can
upgrade from the file.
Upgrade: Click upgrade to begin the upload process. This process may take up to three
minutes.
Warning:
DO NOT power down the router or interrupt the firmware upgrade while it is still in process.
Improper operation may damage the router. Please see section 2.4 for emergency recovery
procedures.
Page 91
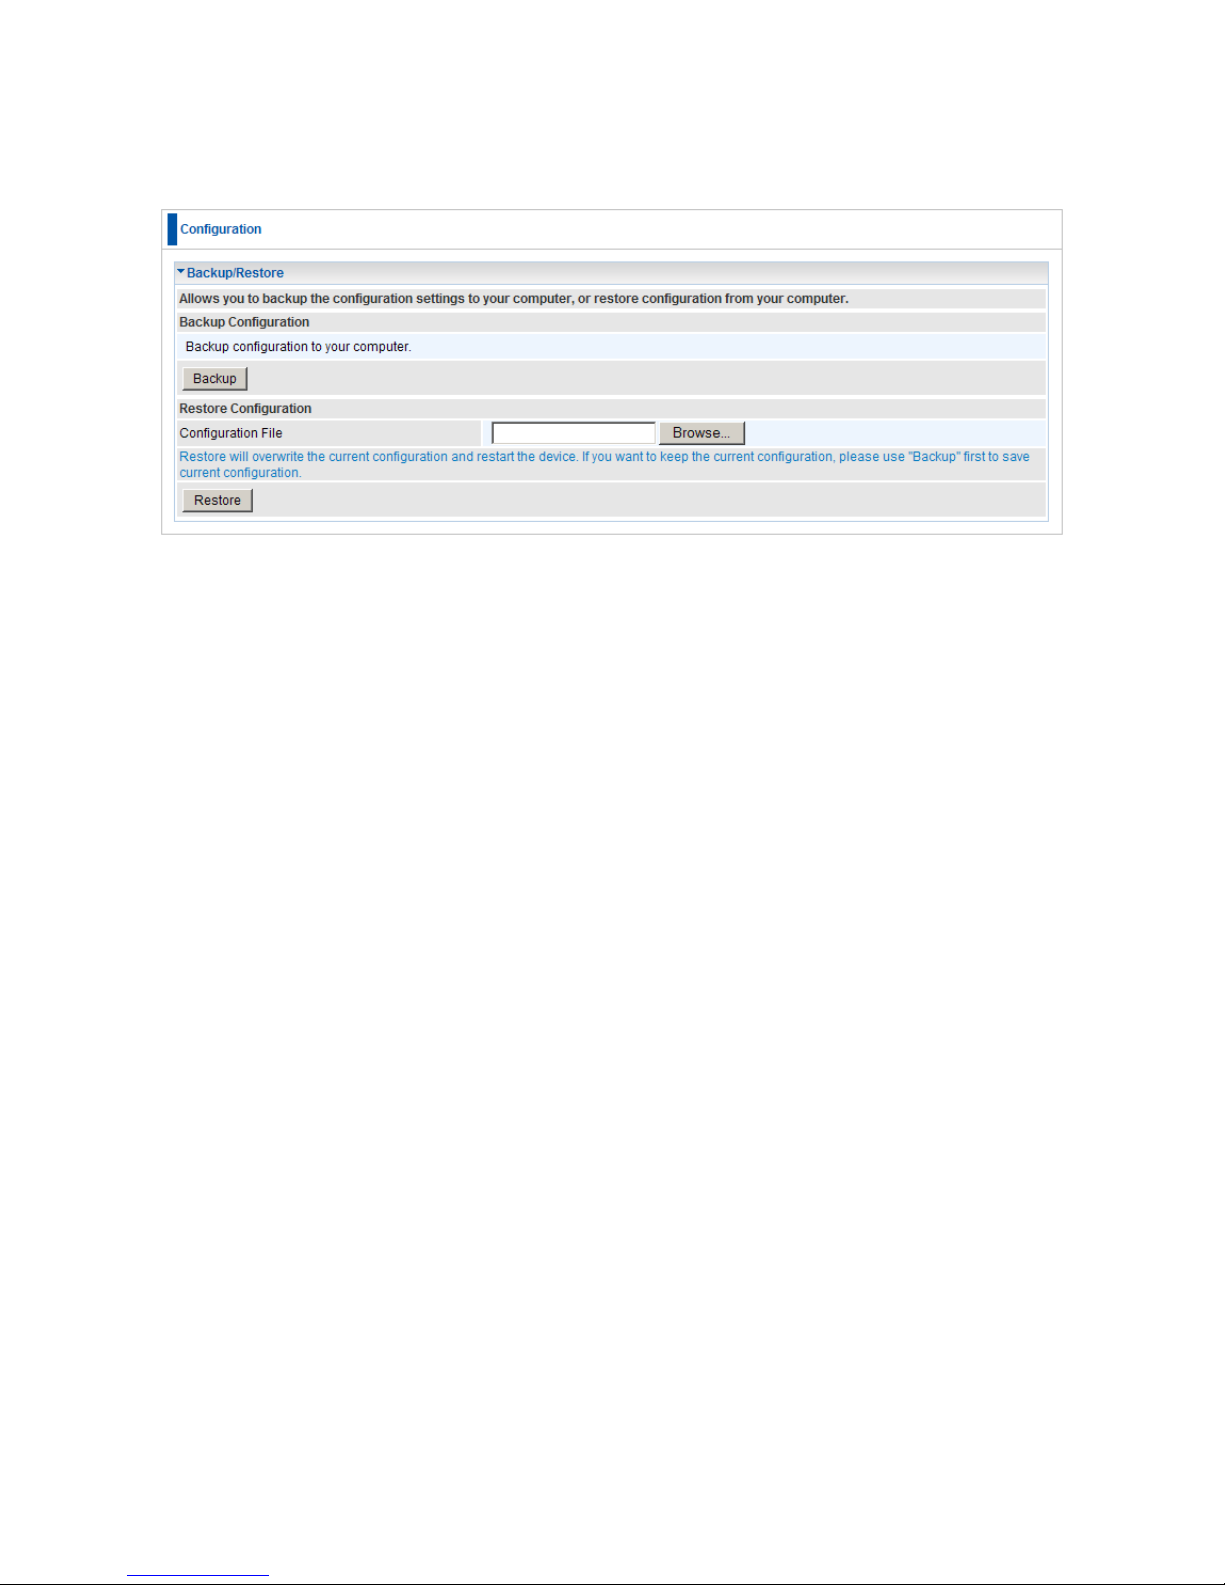
91
Backup / Restore
These functions allow you to save and backup your router‟s current settings to a file on your
PC, or to restore a previously saved backup. This is useful if you wish to experiment with
different settings, knowing that you have a backup handy in the case of any mistakes. It is
advisable to backup your router‟s settings before making any significant changes to your
router‟s configuration.
Press Backup to select where on your local PC to save the settings file. You may also
change the name of the file when saving if you wish to keep multiple backups.
Press Browse… to select a file from your PC to restore. You should only restore settings
files that have been generated by the Backup function, and that were created when using
the current version of the router‟s firmware. Settings files saved to your PC should not
be manually edited in any way.
Select the settings files you wish to use, and press Restore to load those settings into the
router.
Page 92
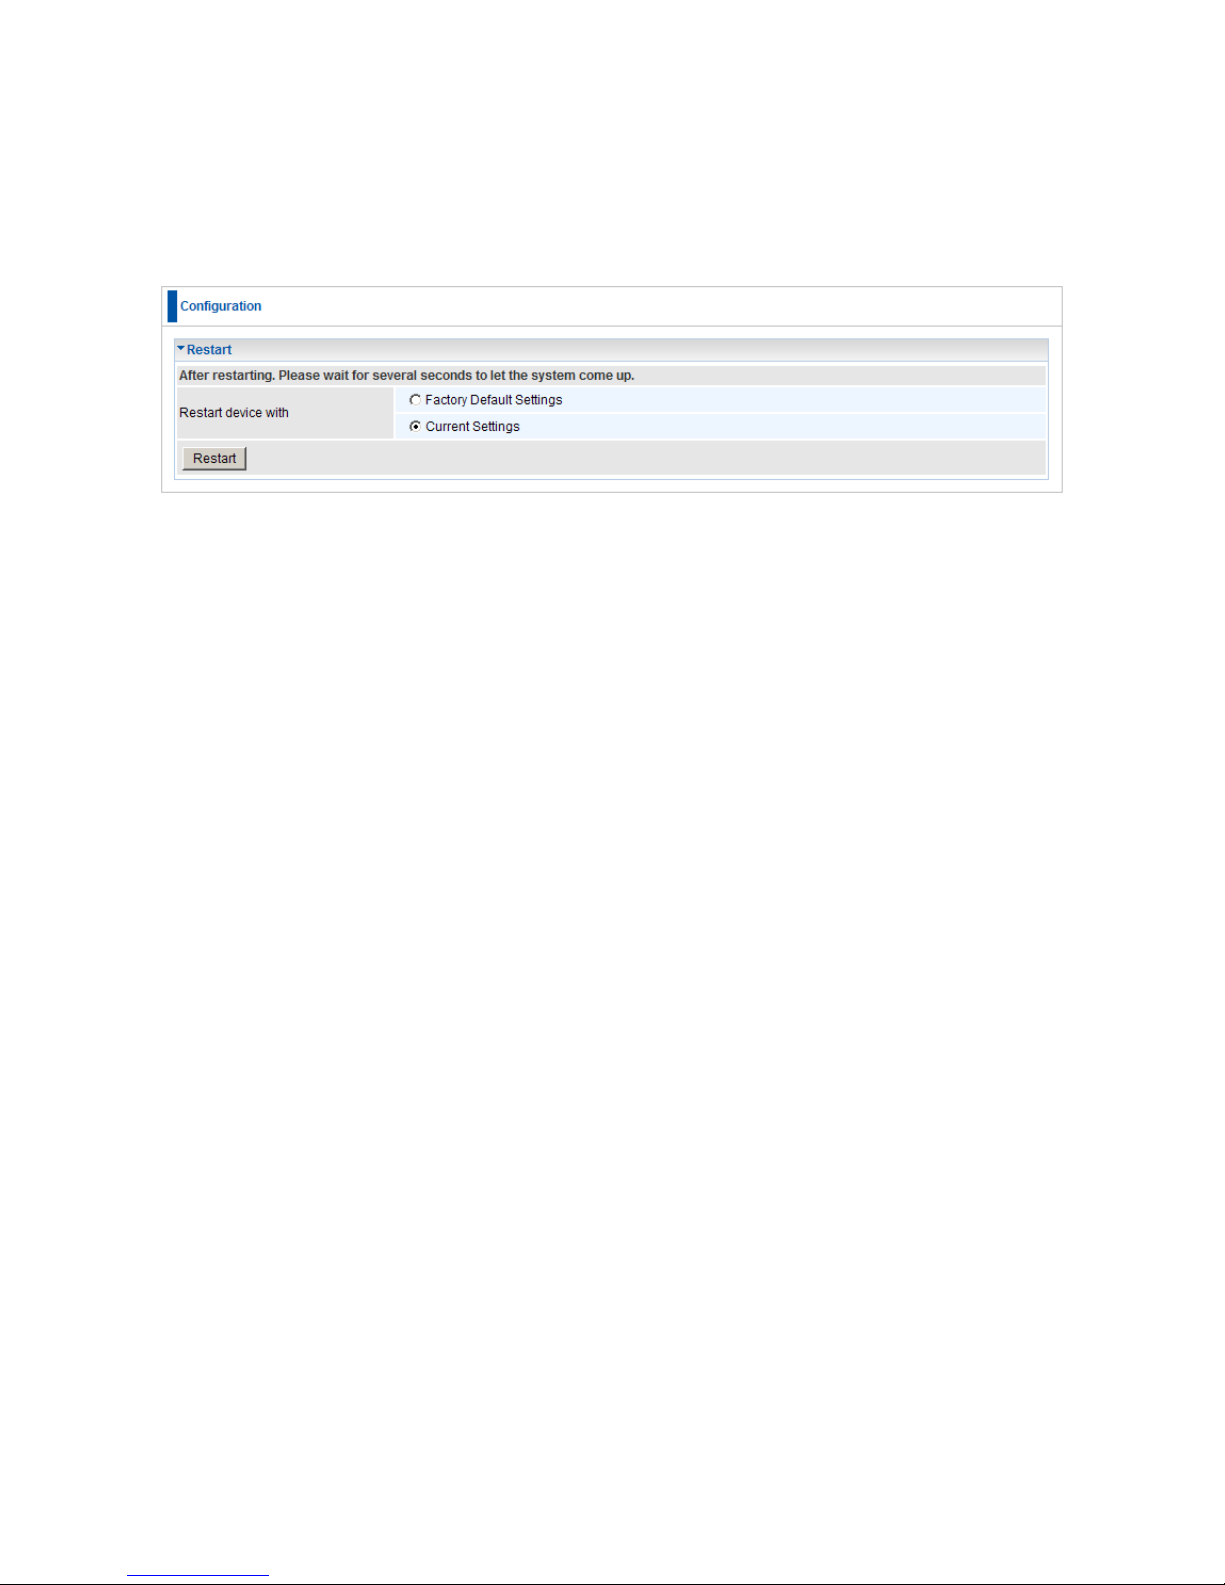
92
Restart Router
Click Restart with option Current Settings to reboot your router and save the current
configuration to device.
If you wish to restart the router using the factory default settings (for example, after a
firmware upgrade or if you have saved an incorrect configuration), select Factory Default
Settings to reset to factory default settings.
Note: IP Address of the router will revert back to default setting of 192.168.0.1.
Page 93
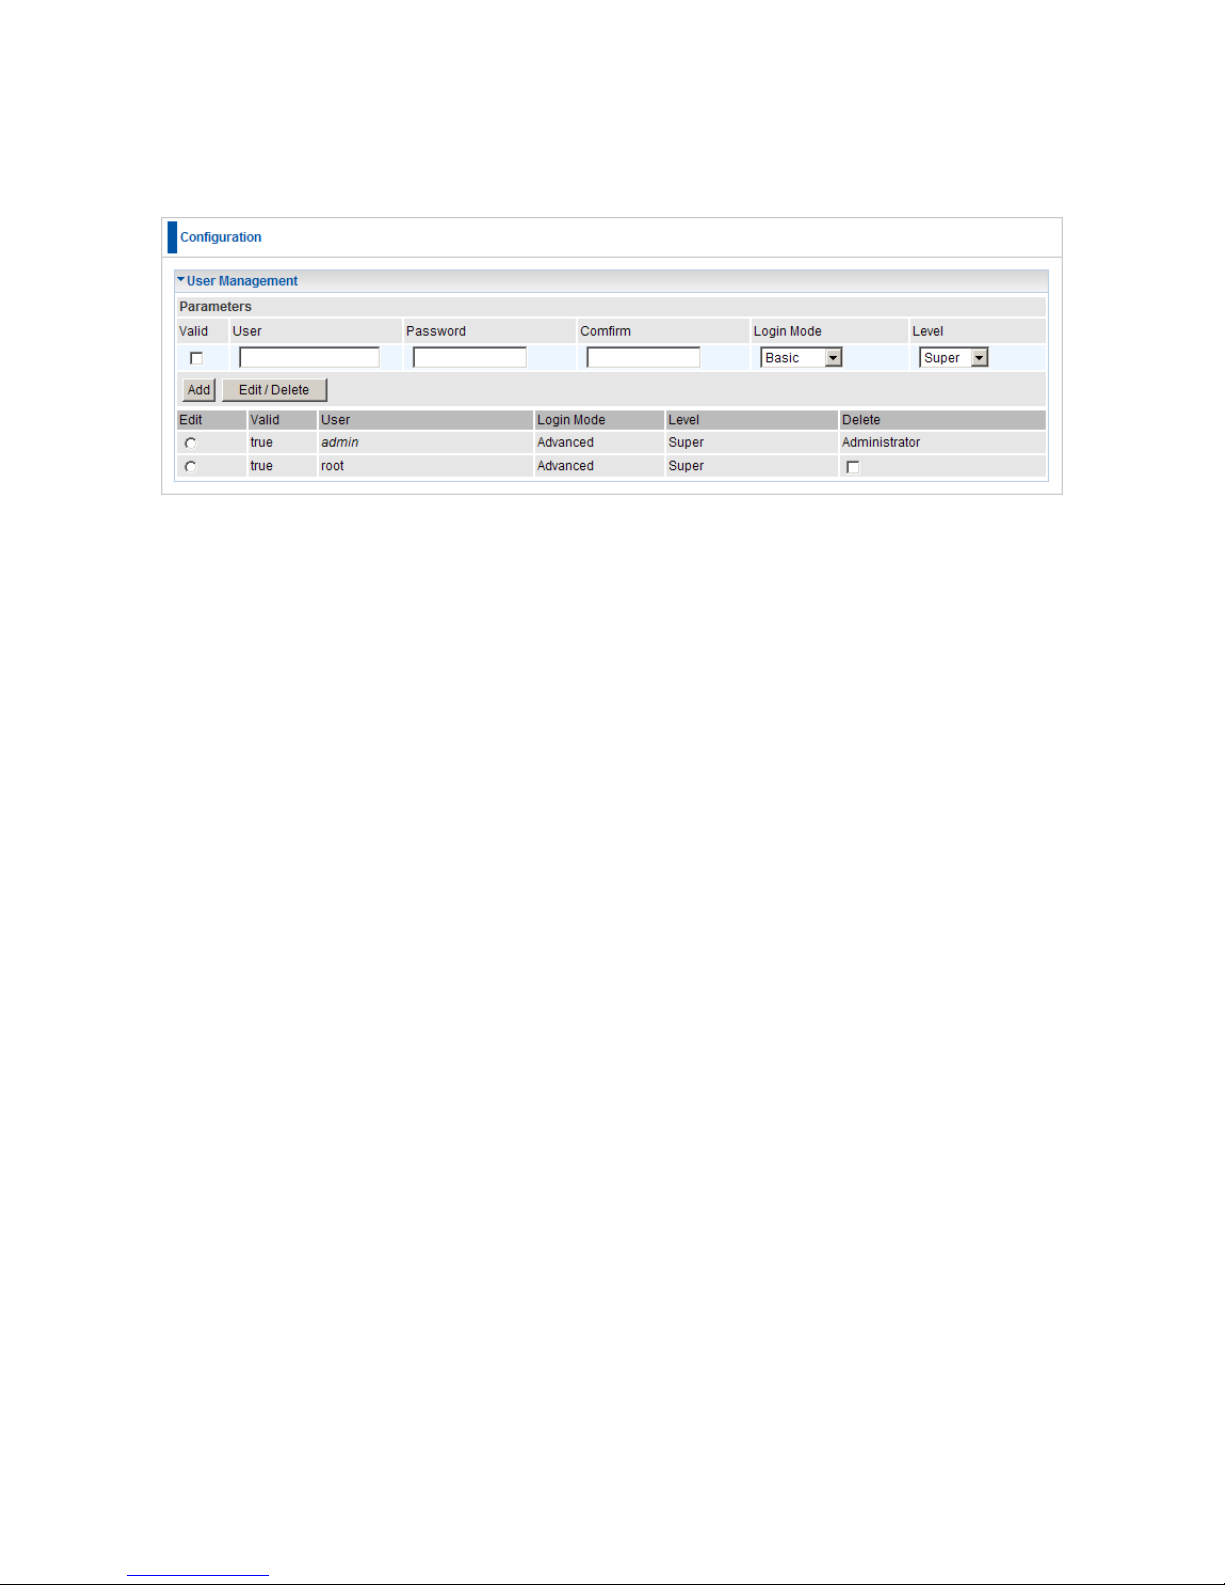
93
User Management
In order to prevent unauthorized access to your router‟s configuration interface, it requires
all users to login with a password. You can set up multiple user accounts, each with their own
password.
You are strongly advised to change the password on the default “admin” account when you
receive your router, and any time you reset your configuration to Factory Defaults.
Valid: Check this box to enable this user account.
User: Username of the user account.
Password: Password of the user account
Confirm: Confirm the password of the user account.
Login Mode: When this account logs in, the Web Interface will be in Basic of Advanced
modes.
Level: To restrict the user account in basic (Normal) or advanced (Super) modes.
Add: Adds a new user account.
Edit: Edit existing user account details. You need to click on the account you want to edit.
Delete: To delete an existing account. Please make sure the tick the delete checkbox.
Page 94
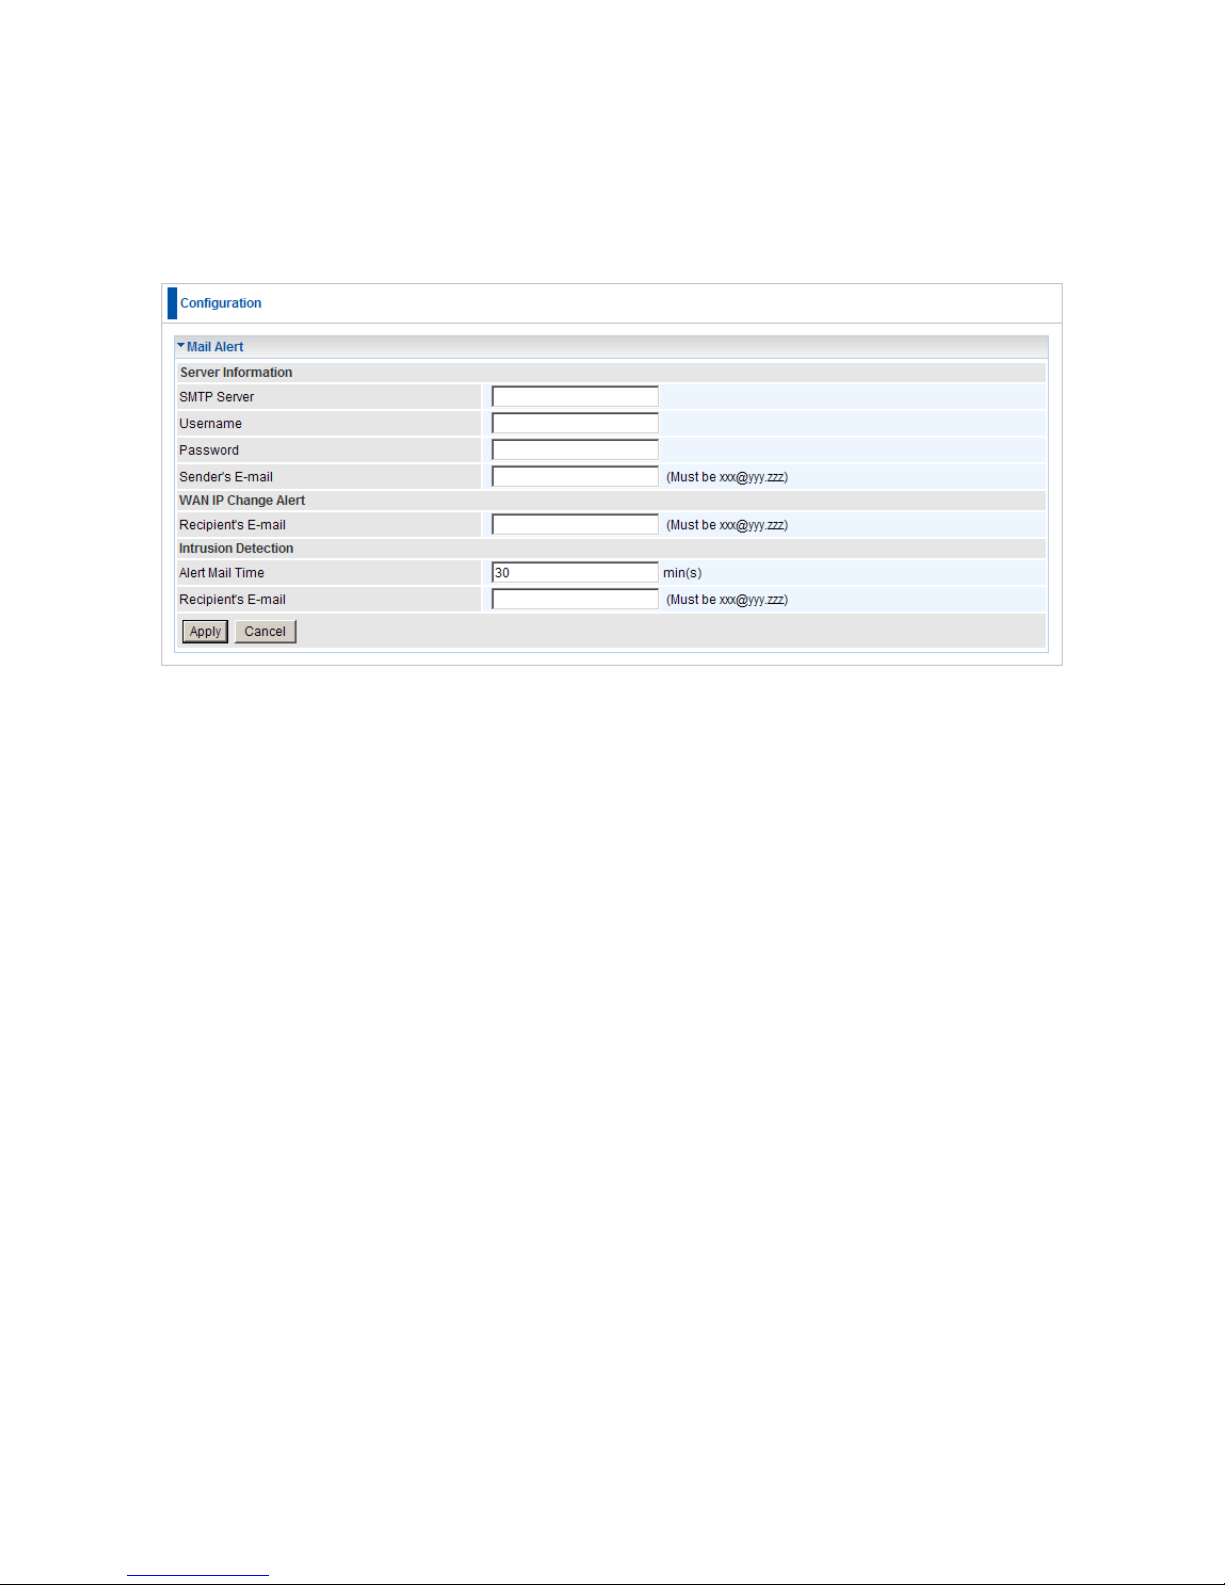
94
Mail Alert
Send a log via email, if WAN IP is changed or if intruders accessing your computer without
permission.
Server Information
SMTP Server: Please enter the address of SMTP mail server for your outgoing emails.
This is usually obtained from your ISP.
Username: Username of your SMTP mail server account.
Password: Password of your SMTP mail server account
Sender’s E-Mail: When the Mail Alert is sent, it will be shown as being sent from this
e-mail address will be shown
WAP IP Change Alert
When your router reconnects to the Internet, the ISP may have given it a new WAN IP
address. When this event happens, an alert e-mail is sent.
Recipient’s E-mail: The e-mail address where the alert email is sent.
Intrusion Detection
When your router detects a Denial of Service in progress, it will send an alert e-mail.
Intrusion Detection needs to be activated in the Firewall settings.
Alert Mail Time: The interval that Intrusion Detection alert e-mails are sent.
Recipient’s E-mail: The e-mail address where the alert email is sent.
Page 95
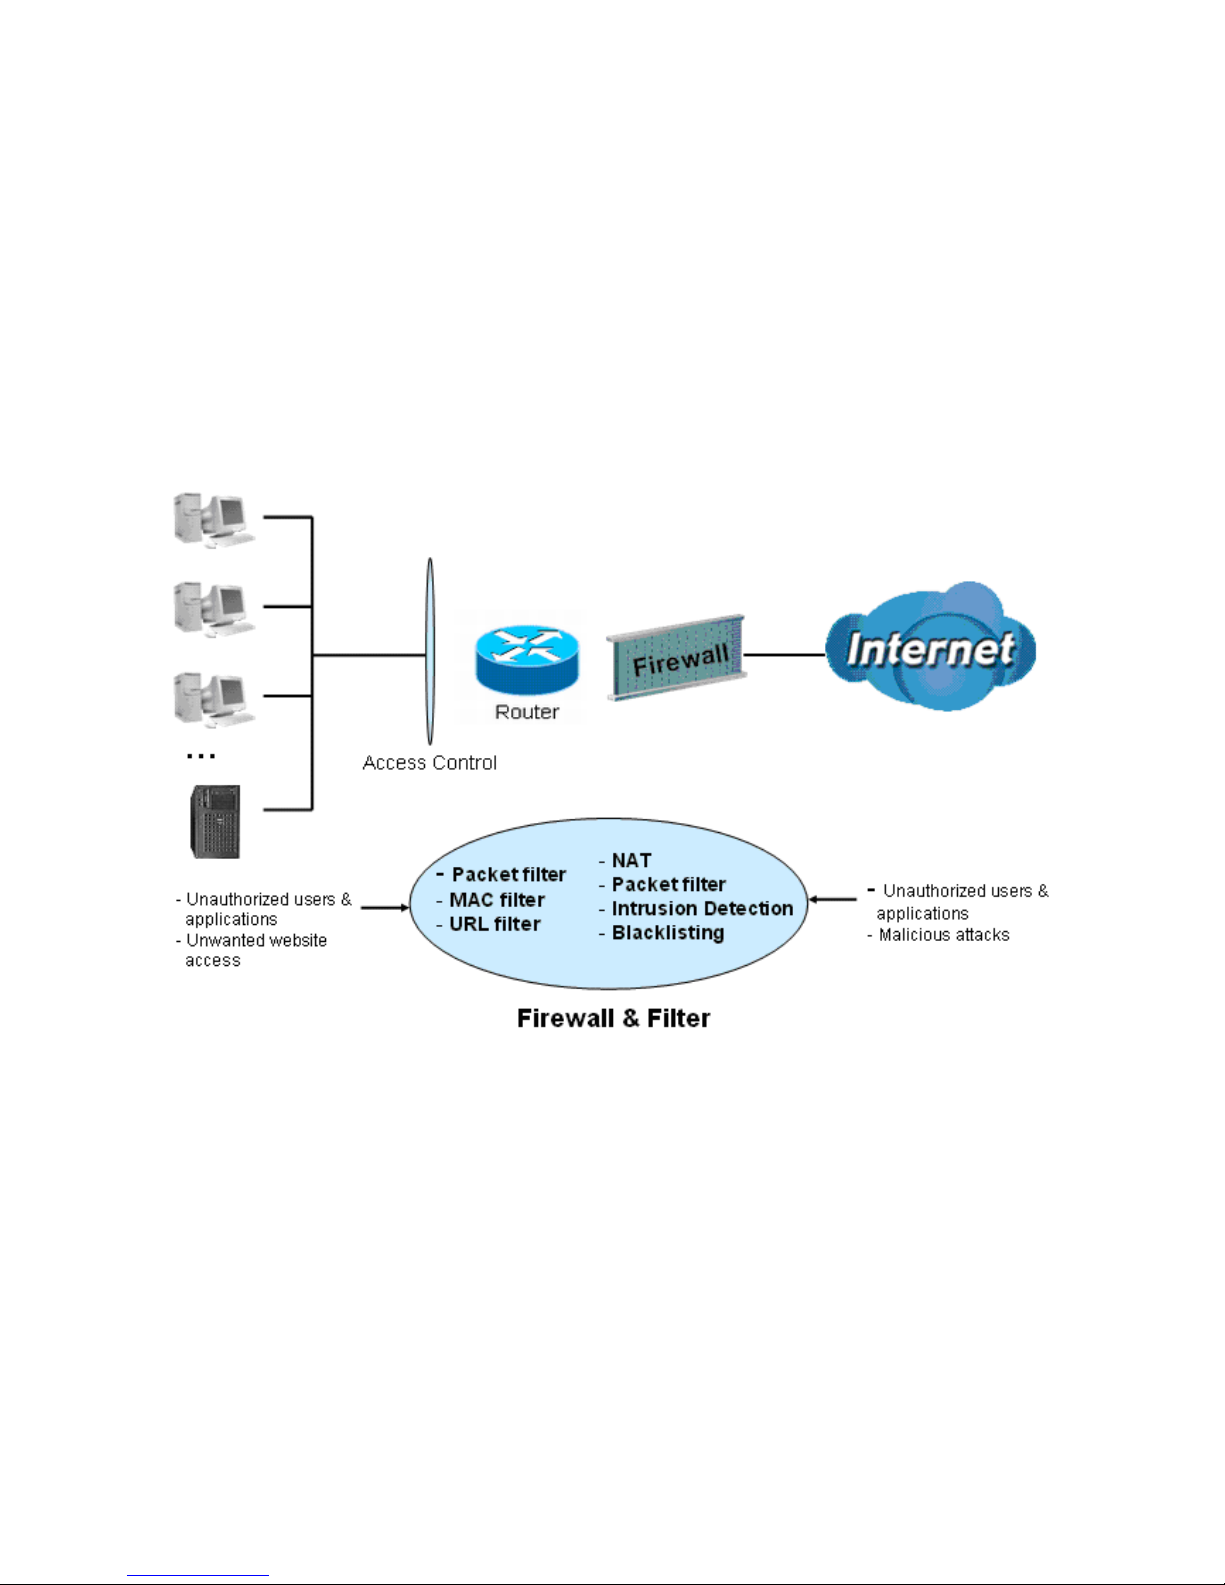
95
Firewall
Firewall and Access Control
Your router includes a full SPI (Stateful Packet Inspection) firewall for controlling Internet
access from your LAN, as well as helping to prevent attacks from hackers. In addition to this,
when using NAT (Network Address Translation) the router acts as a “natural” Internet firewall,
since all PCs on your LAN use private IP addresses that cannot be directly accessed from
the Internet. See the WAN configuration section for more details on NAT.
Firewall: Prevents access from outside your network.
NAT natural firewall: This masks LAN users‟ IP addresses, which are invisible to outside
users on the Internet, making it much more difficult for a hacker to target a machine on your
network. This natural firewall is on when the NAT function is enabled.
Page 96
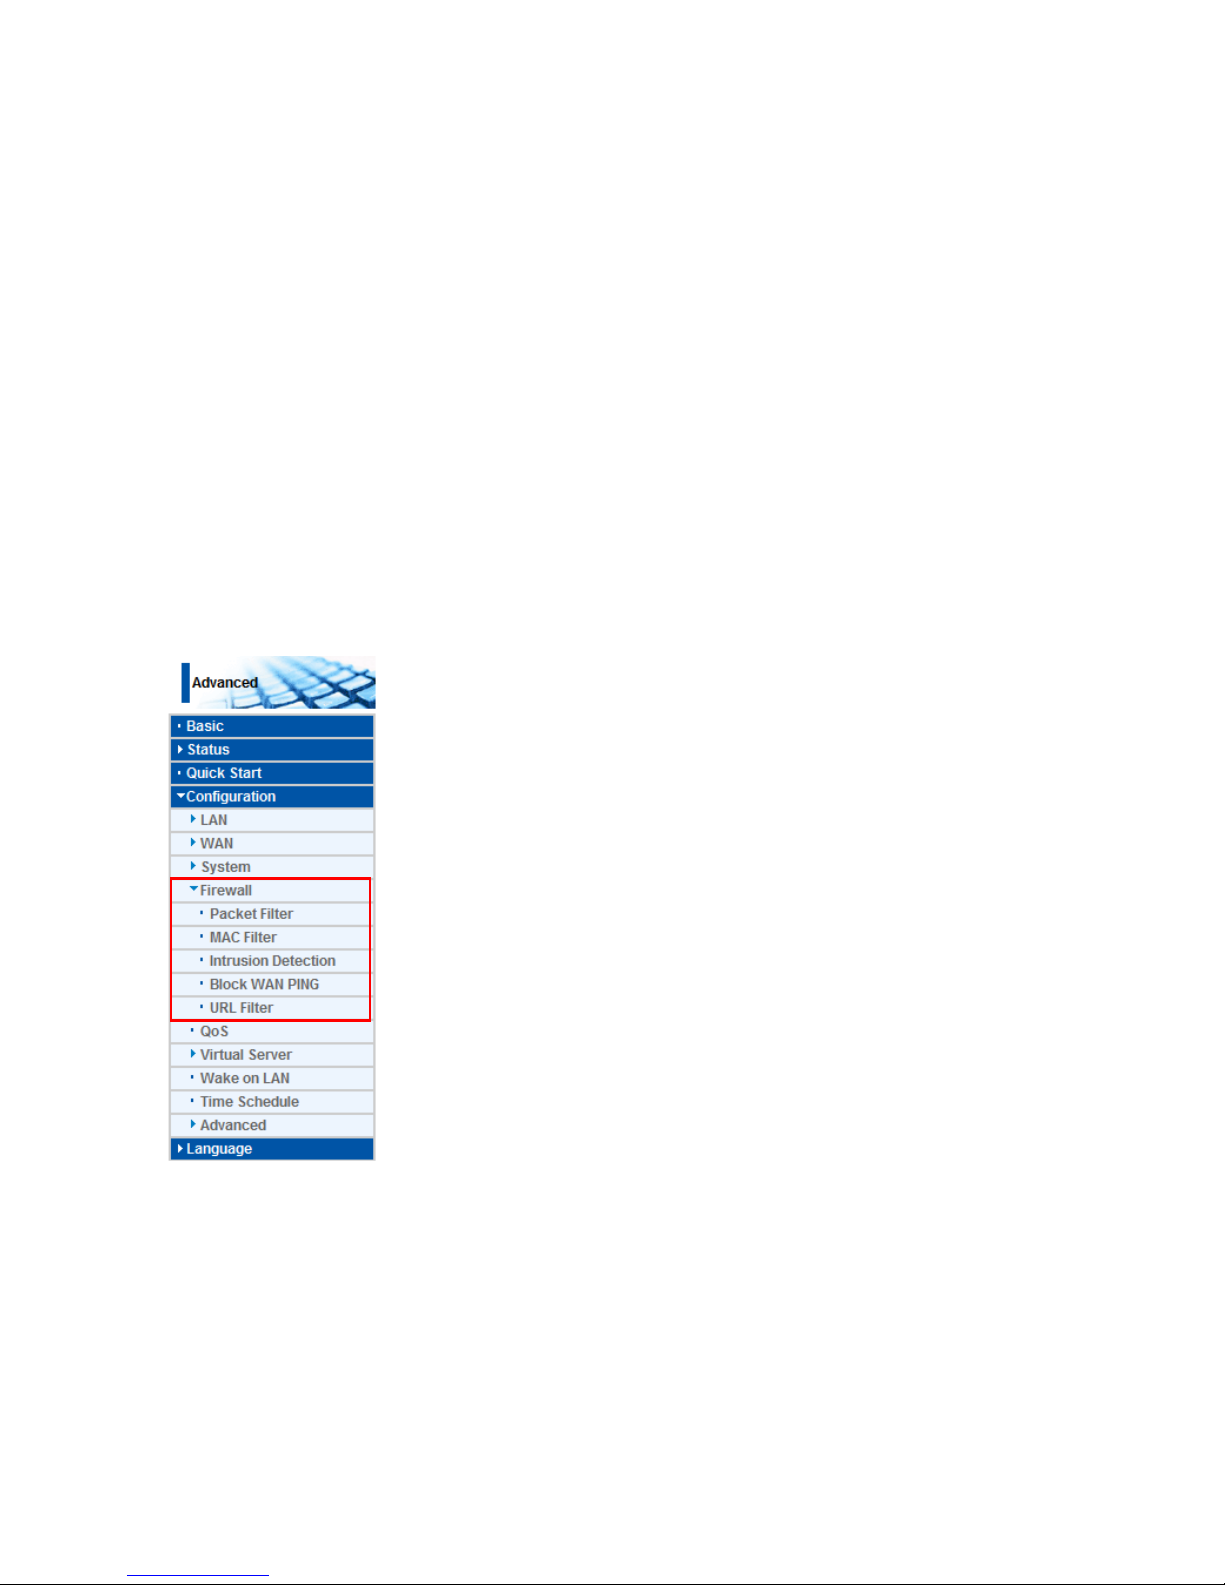
96
Note:
When using Virtual Servers (port mapping) your PCs are exposed to the ports specified
opened in your firewall packet filter settings.
Firewall Security and Policy (General Settings): Inbound direction of Packet Filter
rules prevent unauthorized computers or applications accessing your local network from
the Internet.
Intrusion Detection: Enable Intrusion Detection to detect, prevent, and log malicious
attacks.
MAC Filter rules: Prevents unauthorized computers accessing the Internet.
URL Filter: Blocks PCs on your local network from unwanted websites.
A detailed explanation of each of the following five items appears in the Firewall section
below: Packet Filter, MAC Filter, Intrusion detection, Block WAN PING and URL Filter.
Page 97
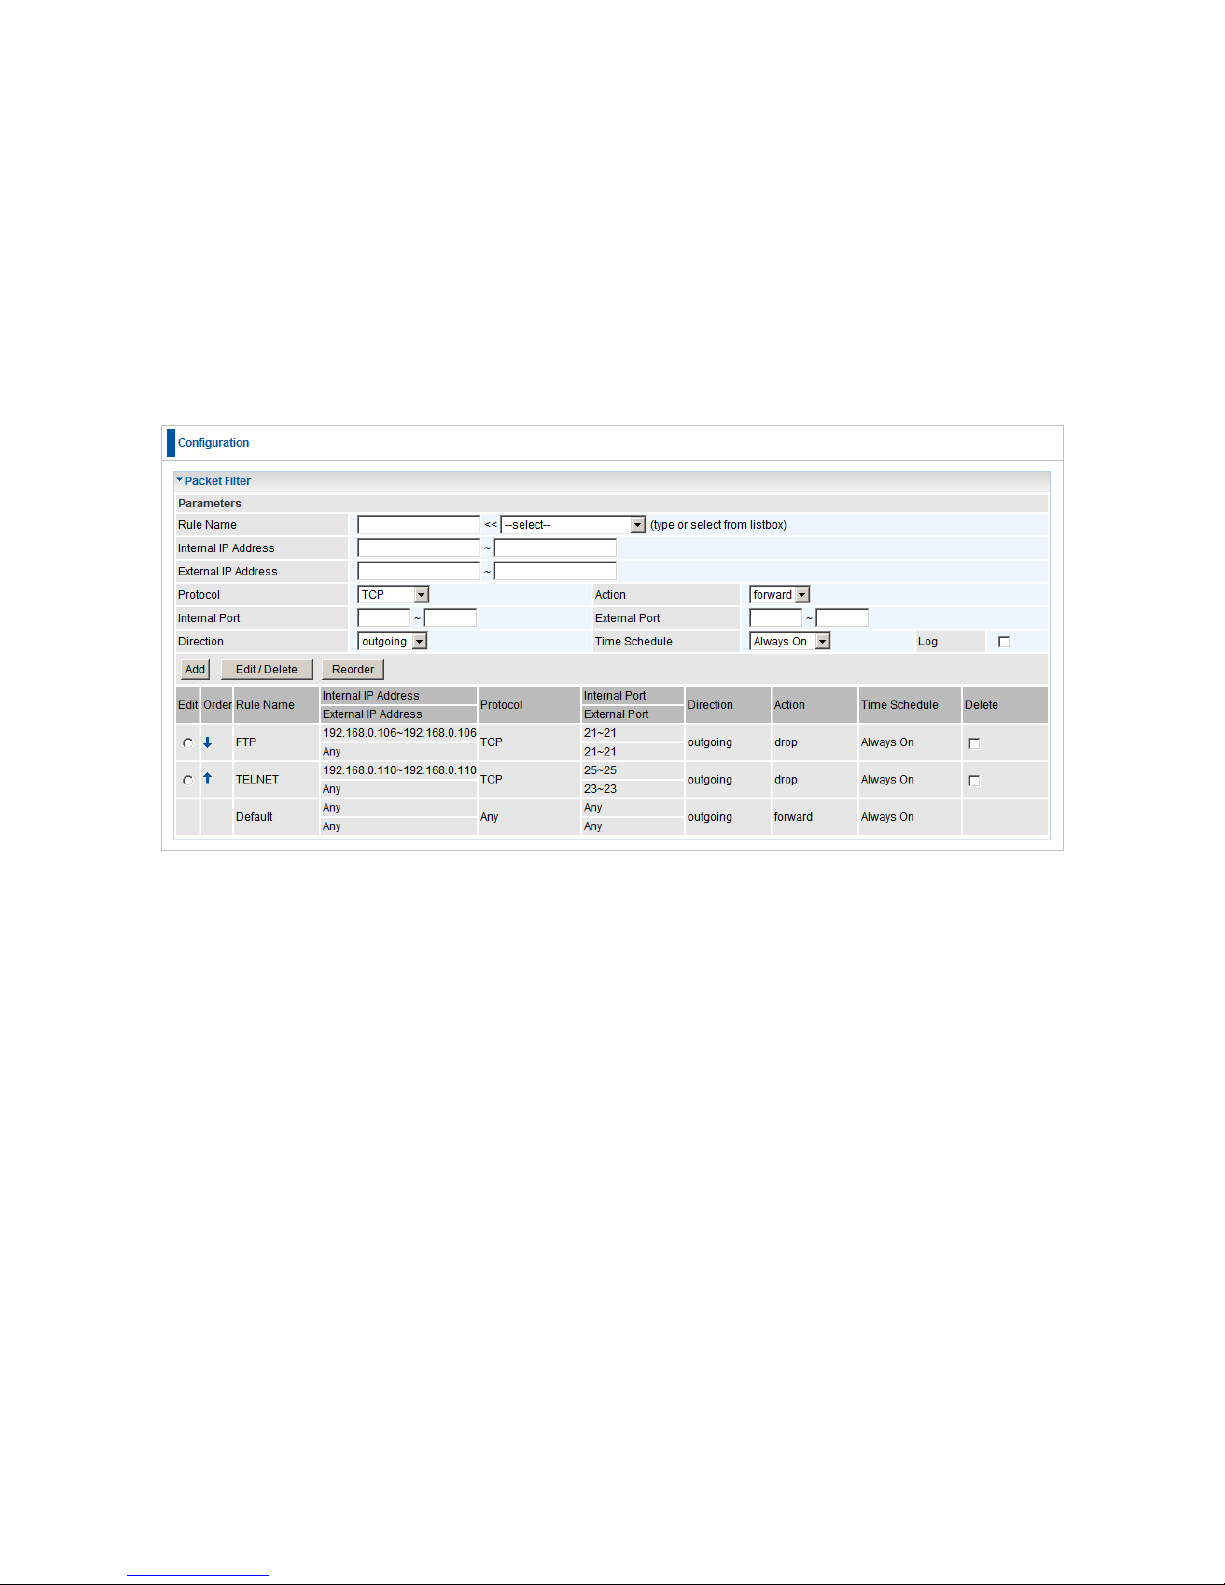
97
Packet Filter
Packet filtering enables you to configure your router to block specified internal/external
users (IP address) from Internet access, or you can disable specific service requests
(Port number) to /from Internet. This configuration program allows you to set up to 6
different filter rules for different users based on their IP addresses or their network Port
number. The relationship among all filters is “or” operation, which means that the router
checks these different filter rules one by one, starting from the first rule. As long as one of
the rules is satisfied, the specified action will be taken.
Rule Name: Users-define description to identify this entry. The maximum name length
is 32 characters, and then can choose application that they want from listbox.
Internal IP Address / External IP Address: This is the Address-Filter used to allow or
block traffic to/from particular IP address(es). Input the range you want to filter out. If
you leave empty or 0.0.0.0, it means any IP address.
Protocol: Specify the packet type (TCP, UDP, ICMP, etc.) that the rule applies to.
Select TCP if you wish to search for the connection-based application service on the
remote server using the port number. Or select UDP if you want to search for the
connectionless application service on the remote server using the port number.
Action: If a packet matches this filter rule, Forward (allows the packets to pass) or
Drop (disallow the packets to pass) this packet.
Internal Port: This Port or Port Range defines the ports allowed to be used by the
Remote/WAN to connect to the application. Default is set from range 0 ~ 65535. It is
recommended that this option be configured by an advanced user.
Page 98
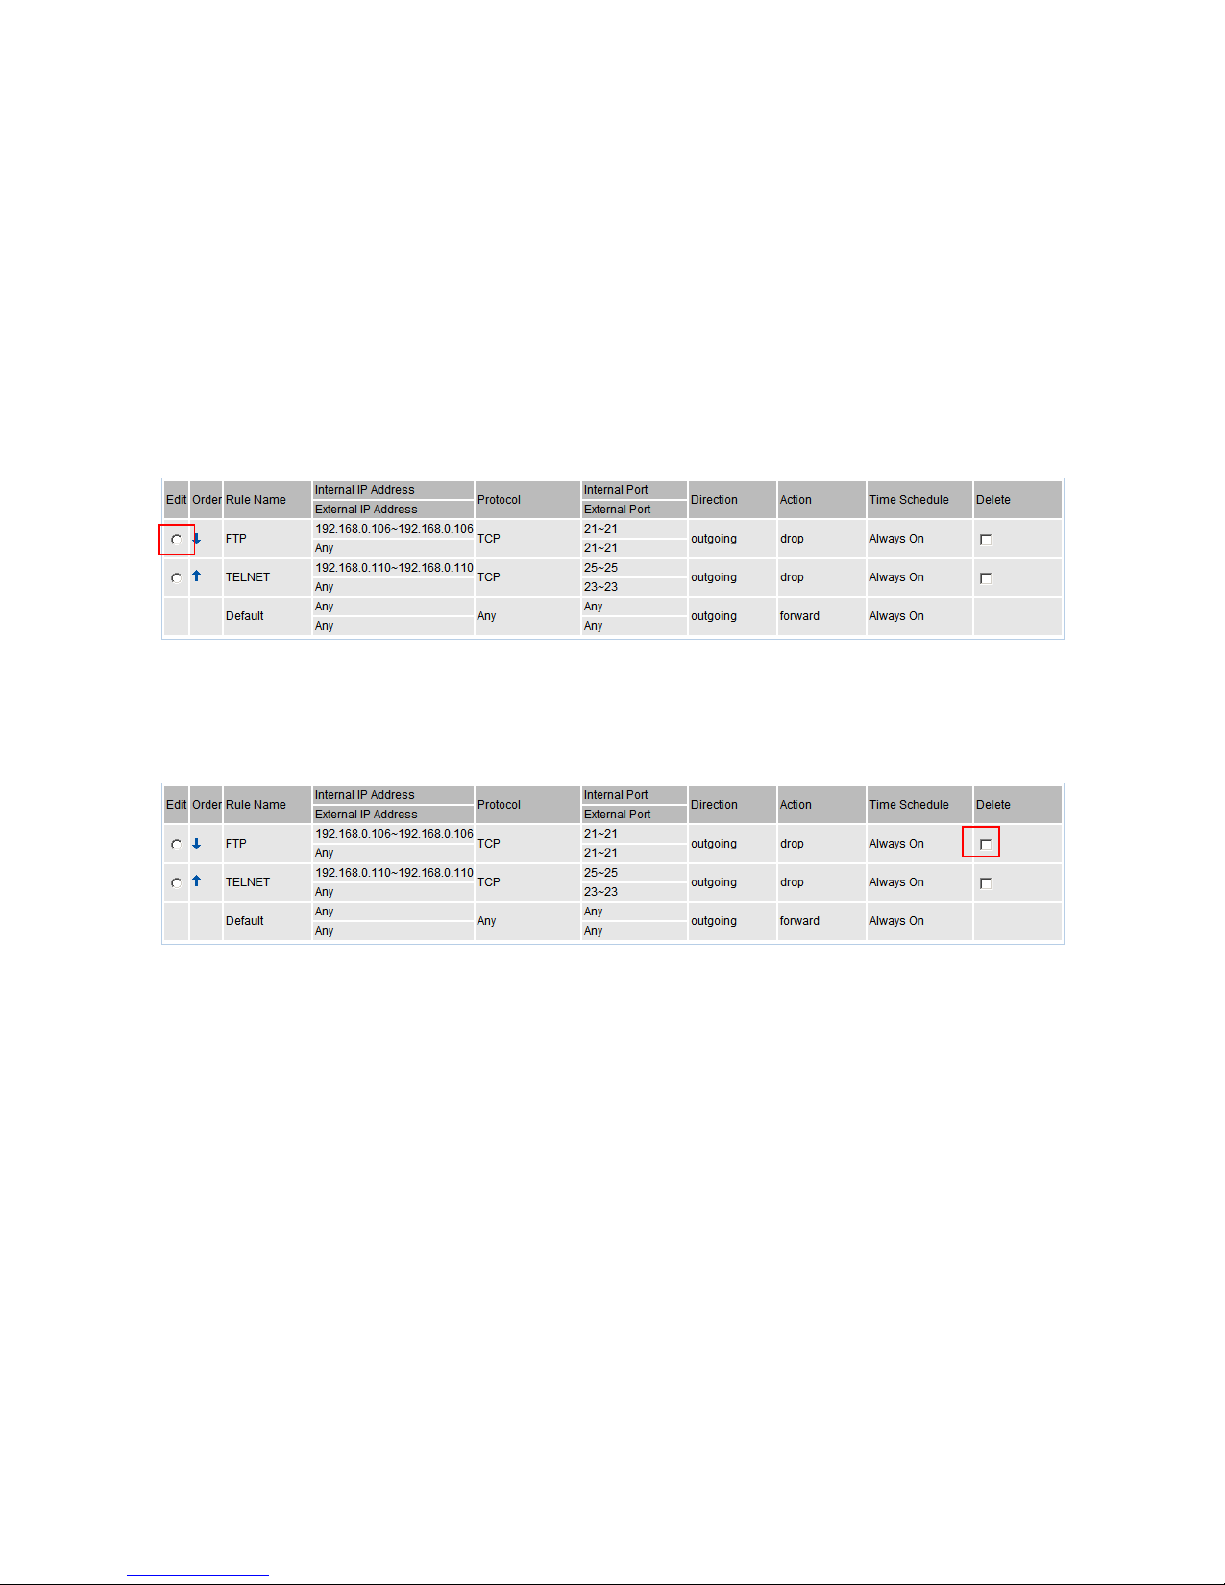
98
External Port: This is the Port or Port Range that defines the application.
Direction: Determine whether the rule is for outgoing packets or for incoming packets.
Time Schedule: It is self-defined time period. You may specify a time schedule for your
prioritization policy. For setup and detail, refer to Time Schedule section.
Log: Choose “log” if you wish to generate logs when the filer rule is applied to a packet.
Add: Click this button to add a new packet filter rule and the added rule will appear at
the bottom table.
Edit: Check the Rule No. you wish to edit, and then click “Edit”.
Order: Use the Up and Down arrows to change the order of the entries.
Delete: First check the Delete tick box of the rule you wish to delete, and then click the
“Edit/Delete” button.
If the DHCP server option is enabled, you must be very careful in assigning IP addresses
of a filtered private IP range to avoid conflicts because you do not know which PC in the
LAN is assigned which IP address. The easiest and safest way is that the filtered IP
address is assigned to a specific PC that is not allowed to access an outside resource
such as the Internet. You configure the filtered IP address manually for this PC, but it
stays in the same subnet with the router.
Page 99
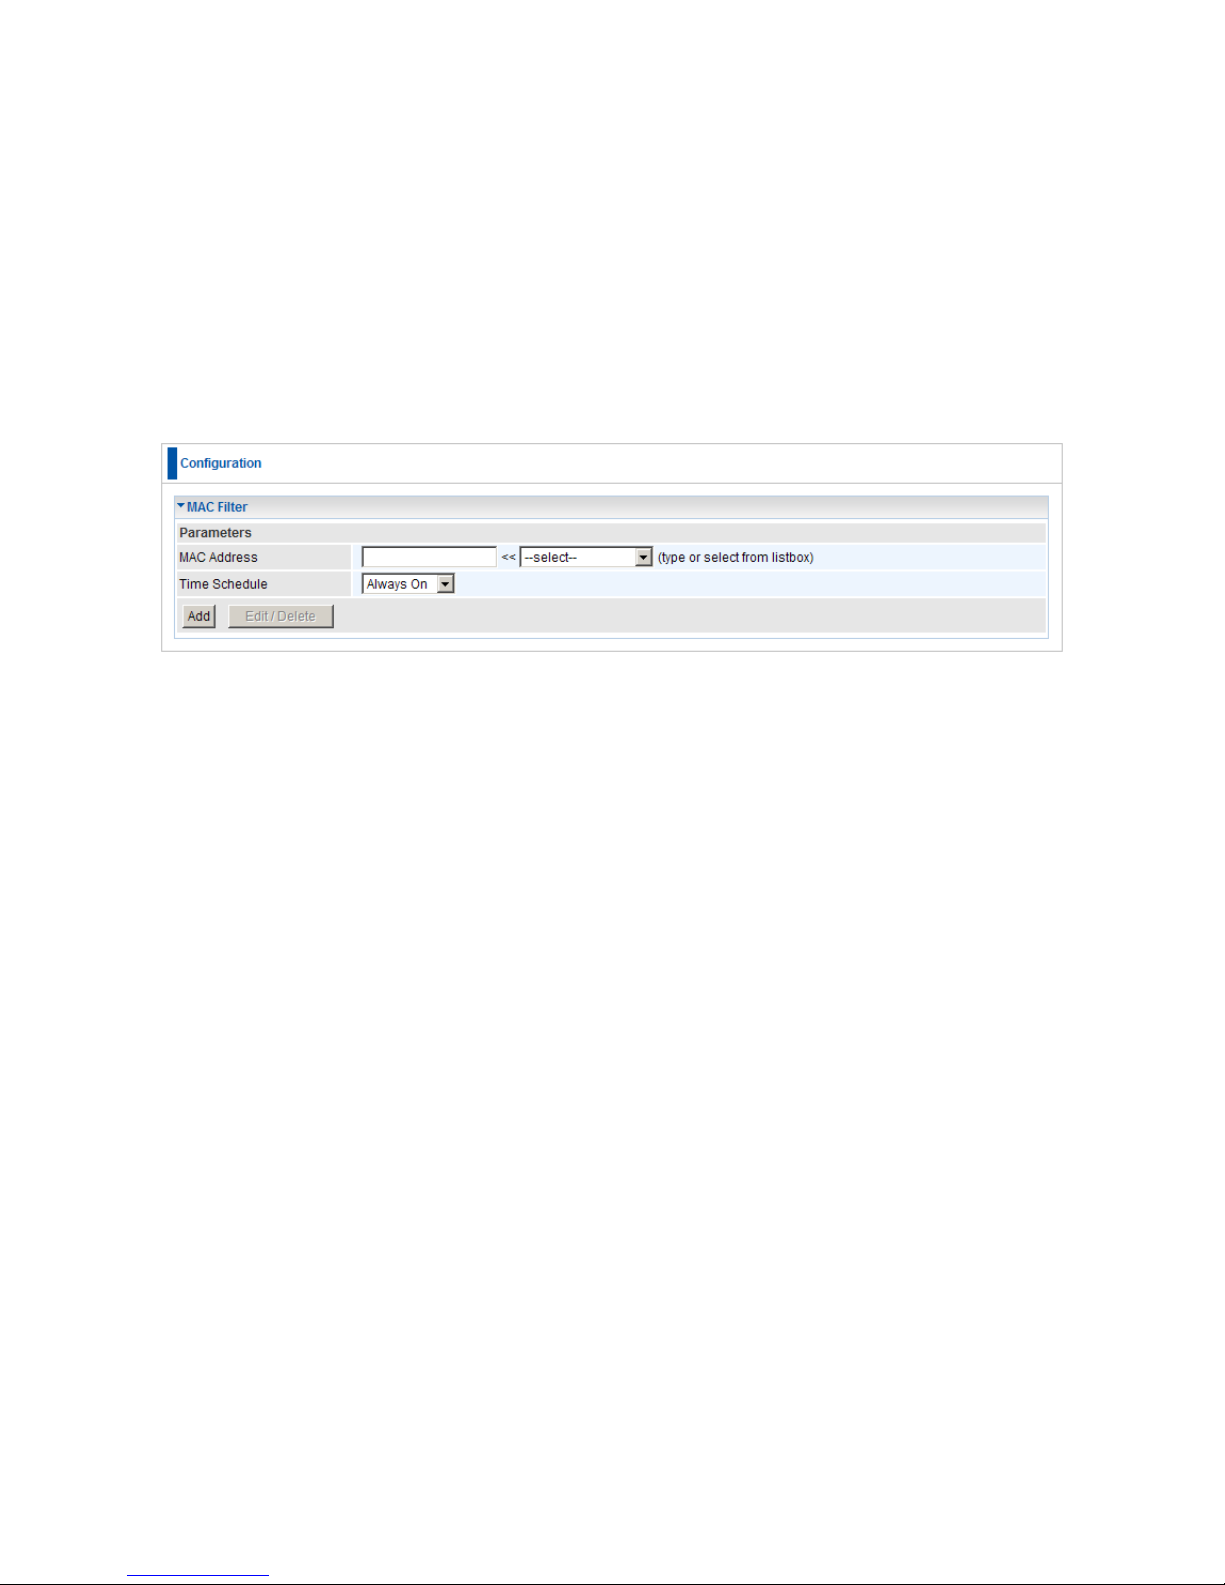
99
MAC Filter
A MAC (Media Access Control) address is the unique network hardware identifier for
each PC on your network‟s interface (i.e. its Network Interface Card or Ethernet card).
Using your router‟s MAC Address Filter function, you can configure to block specific
machines from accessing your LAN.
There are no pre-defined MAC address filter rules; you can add the filter rules to meet
your requirements.
MAC Address: Enter the MAC addresses you wish to filter. You can also use the
selection list box on the right if the router has detected this computer.
Time Schedule: It is self-defined time period. You may specify a time schedule for your
prioritization policy. For setup and detail, refer to Time Schedule section
Page 100
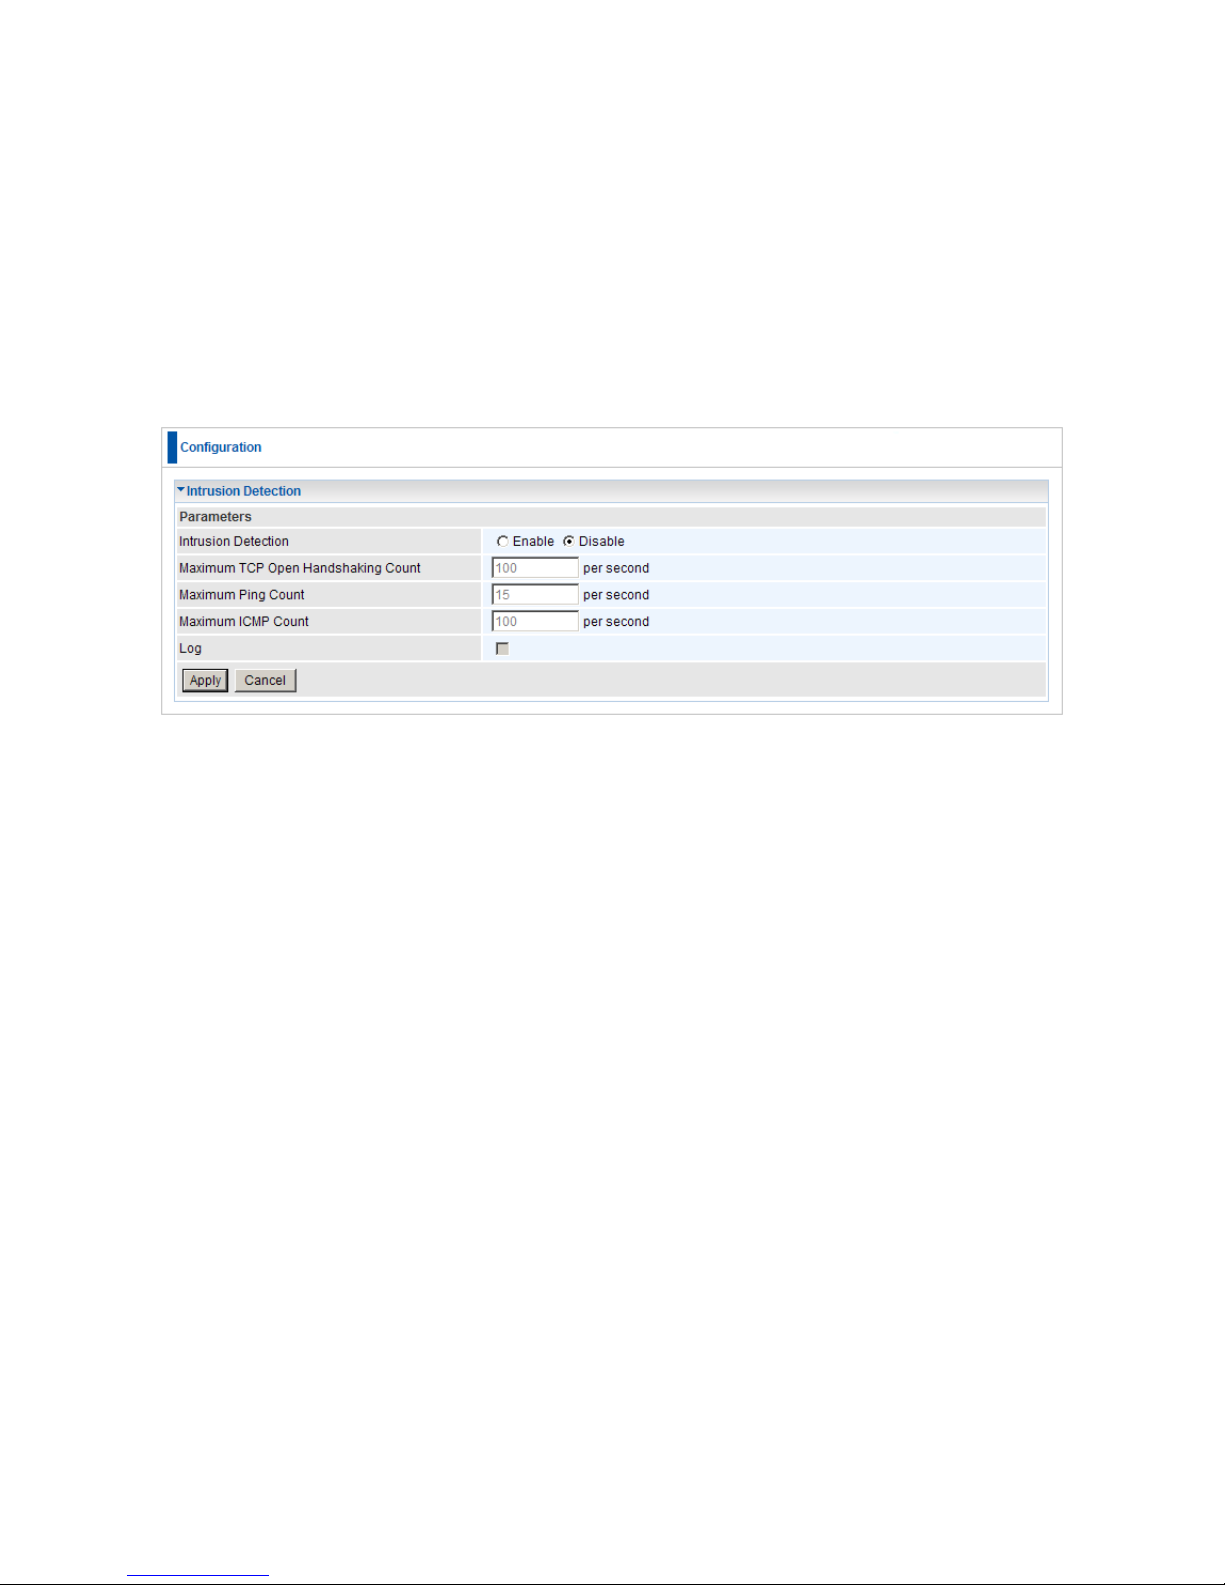
100
Intrusion Detection
Check Enable if you wish to detect intruders accessing your computer without
permission. The router automatically detects and blocks a DoS (Denial of Service)
attack.
This kind of attack is not to access confidential data on the network; instead, it aims to
disrupt specific equipment functions or the operations of entire network. If this happens,
users will have trouble accessing the network resources.
Intrusion Detection: Check Enable if you wish to detect intruders accessing your
computer without permission.
Maximum TCP Open Handshaking Count: This is a threshold value to decide
whether a SYN Flood attempt is occurring or not. Default value is 100 TCP SYN per
seconds.
Maximum Ping Count: This is a threshold value to decide whether an ICMP Echo
Storm is occurring or not. Default value is 15 ICMP Echo Requests (PING) per second.
Maximum ICMP Count: This is a threshold to decide whether an ICMP flood is
occurring or not. Default value is 100 ICMP packets per seconds except ICMP Echo
Requests (PING).
Log: Check Log if you wish to generate logs when the filer rule is applied to the
Intrusion Detection.
 Loading...