

Page 1
GSW-2693
24-Port POE 10/100Mbps plus 2-Port Gigabit TP/SFP
Combo L2 Managed Switch
User Manual
Ver. 1.00-0608
Page 2
ii
The information in this document is subject to change without notice. Unless the explicit written permission of Digital Data
Communications Corporation, this document in whole or in part shall not be replicated or modified or amended or transmitted, in any
from, or by any means manual, electric, electronic, electromagnetic, mechanical, optical or otherwise for any purpose.
DURATION OF HARDWARE WARRANTY
HARDWARE: In accordance with the provisions described under, Digital Data Communications Corporation, (hereinafter called
“LevelOne”) warrants its hardware products (hereinafter referred to as "Product") specified herein to be for a period of twelve (12)
months from the date of shipment.
Should a Product fail to perform during the effective warranty period as described above, LevelOne shall replace the defective
Product or part, or delivering a functionally equivalent Product or part in receipt of customer’s request, provided that the customer
complies with the return material authorization (RMA) procedures and returns all defective Product prior to installation of the
replacements to LevelOne.
All defective Products must be returned to LevelOne with issuance of a Return Material Authorization number (RMA number)
assigned to the reseller from whom the end customer originally purchased the Product. The reseller is responsible for ensuring the
shipments are insured, with the transportation charges prepaid and the RMA number clearly marked on the outside of the package.
LevelOne will not accept collect shipments or those returned without an RMA number.
LevelOne shall not be responsible for any software, firmware, information or memory data contained in, stored on or integrated with
any Product returned to LevelOne pursuant to any warranty.
EXCLUSIONS. The warranty as mentioned above does not apply to the following conditions, in LevelOne’s judgment, it contains (1)
customer does not comply with the manual instructions offered by LevelOne in installation, operation, repair or maintenance, (2)
Product fails due to damage from unusual external or electrical stress, shipment, storage, accident, abuse or misuse, (3) Product is
used in an extra hazardous environment or activities, (4) any serial number on the Product has been removed or defaced, (5) this
warranty will be of no effect if the repair is via anyone other than LevelOne or the approved agents, or (6) In the event of any failures
or delays by either party hereto in the performance of all or any part of this agreement due to acts of God, war, riot, insurrection,
national emergency, strike, embargo, storm, earthquake, or other natural forces, or by the acts of anyone not a party to this
agreement, or by the inability to secure materials or transportation, then the party so affected shall be executed from any further
performance for a period of time after the occurrence as may reasonably be necessary to remedy the effects of that occurrence, but
in no event more than sixty (60) days. If any of the stated events should occur, Party A shall promptly notify Party B in writing as soon
as commercially practicable, but in no event more than twenty (20) business days and provide documentation evidencing such
occurrence. In no event shall the maximum liability of LevelOne under this warranty exceed the purchase price of the Product
covered by this warranty.
DISCLAIMER. EXCEPT AS SPECIFICALLY PROVIDED ABOVE AS REQUIRED “AS IS” AND THE WARRANTIES AND REMEDIES
STATED ABOVE ARE EXCLUSIVE AND IN LIEU OF ALL OTHERS, ORAL OR WRITTEN, EXPRESS OR IMPLIED. ANY AND ALL
OTHER WARRANTIES, INCLUDING IMPLIED WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE
AND NONINFRINGEMENT OR THIRD PARTY RIGHTS ARE EXPRESSLY EXCLUDED.
LEVELONE SOFTWARE LICENSE AGREEMENT
NOTICE: Please carefully read this Software License Agreement (hereinafter referred to as this “Agreement”) before copying or using
the accompanying software or installing the hardware unit with pre-enabled software or firmware (each of which is referred to as
“Software” in this Agreement). BY COPYING OR USING THE SOFTWARE, YOU ACCEPT ALL OF THE PROVISIONS AND
CONDITIONS OF THIS AGREEMENT. THE PROVISIONS EXPRESSED IN THIS AGREEMENT ARE THE ONLY PROVISION
UNDER WHICH LEVELONE WILL PERMIT YOU TO USE THE SOFTWARE. If you do not accept these provisions and conditions,
please immediately return the unused software, manual and the related product. Written approval is NOT a prerequisite to the validity
or enforceability of this Agreement and no solicitation of any such written approval by or on behalf of LevelOne shall be deemed as an
inference to the contrary.
LICENSE GRANT. The end user (hereinafter referred to as “Licensee”) of the Software is granted a personal, non-sublicensable,
nonexclusive, nontransferable license by Digital Data Communications Corporation (“LevelOne”): (1) To use the LevelOne’s software
(“Software”) in object code form solely on a single central processing unit owned or leased by Licensee or otherwise embedded in the
equipment offered by LevelOne. (2) To copy the Software only for backup purposes in support of authorized use of the Software. (3)
To use and copy the documentation related to the Software solely in support of authorized use of the Software by Licensee. The
License applies to the Software only except other LevelOne’s software or hardware products. Without the prior written consent of
LevelOne, Licensee has no right to receive any source code or design documentation with respect to the Software.
RESTRICTIONS ON USE; RESERVATION OF RIGHTS. The Software and related documentation are protected under copyright
laws. LevelOne and/or its licensors retain all title and ownership in both the Software and its related documentation, including any
revisions made by LevelOne. The copyright notice must be reproduced and included with any copy of any portion of the Software or
related documentation. Except as expressly authorized above, Licensee shall not copy or transfer the Software or related
documentation, in whole or in part. Licensee also shall not modify, translate, decompile, disassemble, use for any competitive
analysis, reverse compile or reverse assemble all or any portion of the Software, related documentation or any copy. The Software
and related documentation embody LevelOne’s confidential and proprietary intellectual property. Licensee is not allowed to disclose
the Software, or any information about the operation, design, performance or implementation of the Software and related
documentation that is confidential to LevelOne to any third party. Software and related documentation may be delivered to you subject
to export authorization required by governments of Taiwan and other countries. You agree that you will not export or re-export any
Software or related documentation without the proper export licenses required by the
Page 3
iii
governments of affected countries.
LIMITED SOFTWARE WARRANTY. LevelOne warrants that any media on which the Software is recorded will be free from defects
in materials under normal use for a period of twelve (12) months from date of shipment. If a defect in any such media should occur
during the effective warranty period, the media may be returned to LevelOne, then LevelOne will replace the media. LevelOne shall
not be responsible for the replacement of media if the failure of the media results from accident, abuse or misapplication of the media.
EXCLUSIONS. The warranty as mentioned above does not apply to the Software, which (1) customer does not comply with the
manual instructions offered by LevelOne in installation, operation, or maintenance, (2) Product fails due to damage from unusual
external or electrical stress, shipment, storage, accident, abuse or misuse, (3) Product is used in an extra hazardous environment or
activities, (4) any serial number on the Product has been removed or defaced, or (5) this warranty will be of no effect if the repair is
via anyone other than LevelOne or the authorized agents. The maximum liability of LevelOne under this warranty is confined to the
purchase price of the Product covered by this warranty.
DISCLAIMER. EXCEPT AS PROVIDED ABOVE, THE SOFTWARE IS PROVIDED “AS IS ” AND LEVELONE AND ITS LICENSORS
MAKE NO WARRANTIES, EXPRESS OR IMPLIED, WITH REPSECT TO THE SOFTWARE AND DOCUMENTAITON. LEVELONE
AND ITS LICENSORS DISCLAIM ALL OTHER WARRANTIES, INCLUSIVE OF WITHOUT LIMITATION, IMPL IED WARRANTIES OR
MERCHANTABILITY, FITNESS FOR A PA RTICULAR PURPOSE AND NONINFRINGEMENT. FURTHER, LEVELONE DOES NOT
WARRANT, GUARANTEE, OR MAKE ANY REPRESENTATIONS REGARDING THE USE, OR THE RESULTS OF THE USE, OF
THE SOFTWARE OR RELATED WRITTEN DOCUMENTAITON IN TERMS OF CORRECTNESS, ACCURACY, RELIABILITY, OR
OTHERWISE.
CONSEQUENTIAL DAMAGES. IN NO EVENT SHALL LEVELONE OR ITS AUTHORIZED RESELLER BE LIABLE TO LICENSEE
OR ANY THIRD PARTY FOR (A) ANY MATTER BEYOND ITS REASONABLE CONTROL OR (B) ANY CONSEQUENTIAL, SPECIAL,
INDIRECT OR INCIDENTAL DAMAGES ARISING OUT OF THIS LICENSE OR USE OF THE SOFTWARE PROVIDED BY
LEVELONE, EVEN IF LEVELONE HAS BEEN NOTIFIED OF THE POSSIBILITY OF SUCH DAMAGES IN ADVANCE. IN NO
EVENT SHALL THE LIABILITY OF LEVELONE IN CONNECTION WITH THE SOFTWARE OR THIS AGREEMENT EXCEED THE
PRICE PAID TO LEVELONE FOR THE LICENSE.
TERM AND TERMINATION. The License is effective until terminated; however, all of the restrictions in regard to LevelOne’s
copyright in the Software and related documentation will cease being effective at the date of expiration; Notwithstanding the
termination or expiration of the term of this agreement, it is acknowledged and agreed that those obligations relating to use and
disclosure of LevelOne’s confidential information shall survive. Licensee may terminate this License at any time by destroying the
software together with all copies thereof. This License will be immediately terminated if Licensee fails to comply with any term and
condition of the Agreement. Upon any termination of this License for any reason, Licensee shall discontinue to use the Software and
shall destroy or return all copies of the Software and the related documentation.
GENERAL. This License shall be governed by and construed pursuant to the laws of Taiwan. If any portion hereof is held to be
invalid or unenforceable, the remaining provisions of this License shall remain in full force and effect. Neither the License nor this
Agreement is assignable or transferable by Licensee without LevelOne’s prior written consent; any attempt to do so shall be void.
This License constitutes the entire License between the parties with respect to the use of the Software.
LICENSEE ACKNOWLEDGES THAT LICENSEE HAS READ THIS AGREEMENT, UNDERSTANDS IT, AND AGREES TO BE
BOUND BY ITS TERMS AND CONDITIONS. LICENSEE FURTHER AGREES THAT THIS AGREEMENT IS THE ENTIRE AND
EXCLUSIVE AGREEMENT BETWEEN LEVELONE AND LICENSEE.
Page 4
iv
Caution
Circuit devices are sensitive to static electricity, which can damage their delicate
electronics. Dry weather conditions or walking across a carpeted floor may cause you to
acquire a static electrical charge.
To protect your device, always:
• Touch the metal chassis of your computer to ground the static electrical charge before
you pick up the circuit device.
• Pick up the device by holding it on the left and right edges only.
Electronic Emission Notices
Federal Communications Commission (FCC) Statement
This equipment has been tested and found to comply with the limits for a class A
computing device pursuant to Subpart J of part 15 of FCC Rule s, which are designed to
provide reasonable protection against such interference when operated in a commercial
environment.
European Community (CE) Electromagnetic Compatibility Directive
This equipment has been tested and found to comply with the protection requirements
of European Emission Standard EN55022/EN60555-2 and the Generic European Immunity
Standard EN50082-1.
EMC:
EN55022(1988)/CISPR-22(1985) class A
EN60555-2(1995) class A
EN60555-3
IEC1000-4-2(1995) 4K V CD, 8KV, AD
IEC1000-4-3(1995) 3V/m
IEC1000-4-4(1995) 1KV – (power line), 0.5KV – (signal line)
Page 5
v
About this User Manual
In this user’s manual, it will not only tell you how to install and connect your network
system but configure and monitor the GSW-2693 through the built-in CLI and web by RS-232
serial interface and Ethernet ports step-by-step. Many explanation in detail of hardware and
software functions are shown as well as the examples of the operation for web-based
interface and command-line interface (CLI).
Overview of this user’s manual
Chapter 1 “Introduction” describes the features of GSW-2693
Chapter 2 “Installation”
Chapter 3 “Operation of Web-based Management”
Chapter 4 “Operation of CLI Management”
Chapter 5 “Maintenance”
Page 6
vi
Table of Contents
1. INTRODUCTION...............................................................................................................1
1-1. OVERVIEW .......................................................................................................................1
1-2. CHECKLIST.......................................................................................................................3
1-3. FEATURES........................................................................................................................3
1-4. PHYSICAL OVERVIEW........................................................................................................5
1-4-1. Front Panel.............................................................................................................5
1-4-2. Rear Panel..............................................................................................................7
1-5. OPTIONAL MODULES.........................................................................................................8
2. INSTALLATION ................................................................................................................9
2-1. STARTING UP ...................................................................................................................9
2-1-1. Hardware and Cable Installation ............................................................................9
2-1-2. 19-Inch Wiring Closet Rail....................................................................................11
2-1-3. Cabling Requirements..........................................................................................11
2-1-4. Configuring the Management Agent.....................................................................16
2-1-5. IP Address Assignment.........................................................................................20
2-2. TYPICAL APPLICATIONS ...................................................................................................25
3. OPERATION OF WEB-BASED MANAGEMENT .........................................................27
3-1. OVERVIEW .....................................................................................................................29
3-1-1. System Information...............................................................................................32
3-1-2. IP Configuration....................................................................................................34
3-1-3. Time Configuration ...............................................................................................37
3-1-4. Account Configuration ..........................................................................................40
3-1-5. Management Security...........................................................................................41
3-1-6. Virtual Stack..........................................................................................................44
3-2. PORT CONFIGURATION....................................................................................................46
3-2-1.Port Status.............................................................................................................46
3-2-2. Port Configuration.................................................................................................51
3-2-3. Simple Counter.....................................................................................................53
3-2-4. Detail Counter.......................................................................................................55
3-3. POE...............................................................................................................................58
3-4. LOOP DETECTION ...........................................................................................................62
3-5. SNMP CONFIGURATION..................................................................................................64
3-6. DHCP BOOT..................................................................................................................66
3-7. IGMP SNOOPING............................................................................................................67
3-8. VLAN............................................................................................................................71
3-8-1. VLAN Mode ..........................................................................................................71
3-8-2. Tag-based Group..................................................................................................74
3-8-3. PVID .....................................................................................................................76
3-8-4. Port-based Group.................................................................................................78
3-8-5. Management Vlan ................................................................................................80
3-9. MAC TABLE ...................................................................................................................81
3-10. GVRP CONFIGURATION................................................................................................88
3-11. STP CONFIGURATION ...................................................................................................94
3-11-1. STP Status..........................................................................................................94
3-11-2. STP Configuration...............................................................................................96
3-11-3. STP Port Configuration.......................................................................................98
3-12. TRUNKING CONFIGURATION.........................................................................................101
3-13. 802.1X CONFIGURATION.............................................................................................107
Page 7
vii
3-14. ALARM CONFIGURATION..............................................................................................117
3-15. CONFIGURATION.........................................................................................................120
3-15-1. Save/Restore....................................................................................................121
3-16. SECURITY ..................................................................................................................123
3-17. BANDWIDTH MANAGEMENT .........................................................................................126
3-18. QOS(QUALITY OF SERVICE) CONFIGURATION...............................................................129
3-19. DIAGNOSTICS.............................................................................................................139
3-20. TFTP SERVER............................................................................................................142
3-21. LOG...........................................................................................................................143
3-22. FIRMWARE UPGRADE..................................................................................................144
3-23. REBOOT.....................................................................................................................145
3-24. LOGOUT.....................................................................................................................146
4. OPERATION OF CLI MANAGEMENT.........................................................................147
4-1. CLI MANAGEMENT........................................................................................................147
4-1-1. Login...................................................................................................................147
4-2. COMMANDS OF CLI.......................................................................................................149
4-2-1. Global Commands of CLI...................................................................................151
4-2-2. Local Commands of CLI.....................................................................................157
5. MAINTENANCE............................................................................................................246
5-1. RESOLVING NO LINK CONDITION ...................................................................................246
5-2. Q&A............................................................................................................................246
6. APPENDIX A TECHNICAL SPECIFICATIONS ..........................................................247
7. APPENDIX B NULL MODEM CABLE SPECIFICATIONS.........................................251
Page 8
Page 9
1
1. Introduction
1-1. Overview
GSW-2693, a 24 Fast Ethernet + 2 Gigabit L2 Managed Switch, implemented
24 10/100Mbps TP + 2 Gigabit dual media ports with TP/SFP, is a standard switch
that meets all IEEE 802.3/u/x/z Gigabit, Fast Ethernet and Ethernet specifications.
The switch can be managed through RS-232 serial port via directly connection, or
through Ethernet port using Telnet or Web-based management unit, associated with
SNMP agent. With the SNMP agent, the network administrator can logon the switch
to monitor, configure and control each port’s activity in a friendly way. The overall
network management is enhanced and the network efficiency is also improved to
accommodate high bandwidth applications. In addition, the switch features
comprehensive and useful function such as QoS (Quality of Service), Spanning
Tree, VLAN, Port Trunking, Bandwidth Control, Port Security, SNMP/RMON and
IGMP Snooping capability via the intelligent software. It is suitable for both metroLAN and office application.
This POE switch also complies with IEEE 802.3af, its advanced auto-sensing
algorithm enables providing power devices (PD) discovery, classification, current
limit, and other necessary functions. It also supports high safety with short circuit
protection and power-out auto-detection to PD.
•
Model Description
Model Port 25, 26 Configurations
GSW-2693 Two types of media --- TP and SFP Fiber
10/100/1000Mbps TP is a standard Ethernet port that meets all IEEE
802.3/u/x/z Gigabit, Fast Ethernet specifications. 1000Mbps SFP Fiber transceiver
is a Gigabit Ethernet port that fully complies with all IEEE 802.3z and 1000BaseSX/LX standards.
For upgrading firmware, please refer to the Section 3-21 or Section 4-2-2 for
more details. The switch will not stop operating while upgrading firmware and after
that, the configuration keeps unchanged.
Page 10
2
•
Key Features in the Device
QoS
Support Quality of Service by the IEEE 802.1P standard. There are two priority
queue and packet transmission schedule using W eig hted Round Robin (WRR).
User-defined weight classification of packet priority can be based o n either VLAN
tag on packets or use r-defined port priority.
Spanning Tree
Support IEEE 802.1D, IEEE 802.1w (RSTP: Rapid Spanning Tree Protocol)
standards.
VLAN
Support Port-based VLAN and IEEE802.1Q Tag VLAN. Support 256 active VLANs
and VLAN ID 1~4094.
Port Trunking
Support static port trunking and port trunking with IEEE 802.3ad LACP.
Bandwidth Control
Support ingress and egress per port bandwidth control.
Port Security
Support allowed, denied forwarding and port security with MAC address.
SNMP/RMON
SNMP agent and RMON MIB. In the device, SNMP agent is a client software which
is operating over SNMP protocol used to receive the command from SNMP
manager (server site) and echo the corresponded data, i.e. MIB object. Besides,
SNMP agent will actively issue TRAP information when happened.
RMON is the abbreviation of Remote Network Monitoring and is a branch of the
SNMP MIB. The device support s MIB-2 (RFC 1213), Bridge MIB (RFC 1493),
RMON MIB (RFC 1757)-statistics Group 1,2,3,9, Ethernet-like MIB (RFC 1643),
Ethernet MIB (RFC 1643) and so on.
IGMP Snooping
Support IGMP version 2 (RFC 2236): The function IGMP snooping is used to
establish the multicast groups to forward the multicast packet to the member p orts,
and, in nature, avoid wasting the bandwidth while IP multicast packets are running
over the network.
Page 11
3
1-2. Checklist
Before you start installing the switch, verify that the package contains the
following:
- GSW-2693
- Power Cord
- Rack-mount Kits
- RS-232 Cable
- CD User Manual
Please notify your sales representative immediately if any of the aforementioned
items is missing or damaged.
1-3. Features
The GSW-2693, a standalone off-the-shelf switch, provides the
comprehensive features listed below for users to perform system network
administration and efficiently and securely serve your network.
•
Hardware
• Supports 24-port 10/100M TP ports with Nway and auto MDIX function
• In GSW-2693 switch, it supports 2 Gigabit dual media ports(TP/SFP) and 2 slots
for removable SFP module supporting 1000M SFP fiber module
• Supports on-line pluggable fiber transceiver modules
• Supports 256KB packet buffer and 128KB control memory
• Maximal packet length can be up to 1536 bytes
• Full-duplex flow control (IEEE802.3x) and half-duplex backpressure
• Extensive front-panel diagnostic LEDs; System: Power, CPURUN, ACT / FDX /
SPD(LEDSET), 10/100Mbps TP Port1-24:LINK/ACT, FDX, SPD,
10/100/1000Mbps/Fiber port 25,26: LINK/ACT, FDX, SPD
24 port IEEE802.3af PoE
Endpoint with 48VDC power through RJ-45 pin 1, 2, 3, 6.
Powered Device(PD) auto detection and classification.
PoE-PSE status and activity LED indicator.
Page 12
4
• Management
• Supports concisely the status of port and easily port configuration
• Supports per port traffic monitoring counters
• Supports a snapshot of the syste m Information when you login
• Supports port mirror function
• Supports the static trunk function
• Supports 802.1Q VLAN with 256 entries.
• Supports user management and limits three users to login
• Supports DHCP Broadcasting Suppression to avoid network suspended or
crashed
• Supports to send the trap event while monitored events happened
• Supports default configuration which can be restored to overwrite the current
configuration which is working on via web browser and CLI
• Supports on-line plug/unplug SFP modules
• Supports 5 kinds of QoS, are as follows, MAC Priority, 802.1p Priority, IP TOS
Priority, and DiffServ DSCP Priority.
• Built-in web-based management and CLI management, providing a more
convenient UI for the user
• Supports port mirror function with ingress/egress traffic
• Supports rapid spanning tree (802.1w RSTP)
• Supports 802.1x port security on a VLAN
• Supports user management and only first login a dministrator can configure the
device. The rest of users can only view the switch
• SNMP access can be disabled and prevent from illegal SNMP access
• Supports Ingress, Non-unicast and Egress Bandwidth rating management
• The trap event and alarm message can be transferred via e-mail and mobile
phone short message
• Supports diagnostics to let administrat or knowing the hardware status
• Supports external loopback test to check if the link is ok
• TFTP for firmware upgrade, system log upload and config file imp ort/export
• Supports remote boot the device through user interface and SNMP
• Supports network time synchronization and daylight saving
• Supports 120 event log records in the main memory and display on the local
console
Page 13
5
1-4. Physical Overview
1-4-1. Front Panel
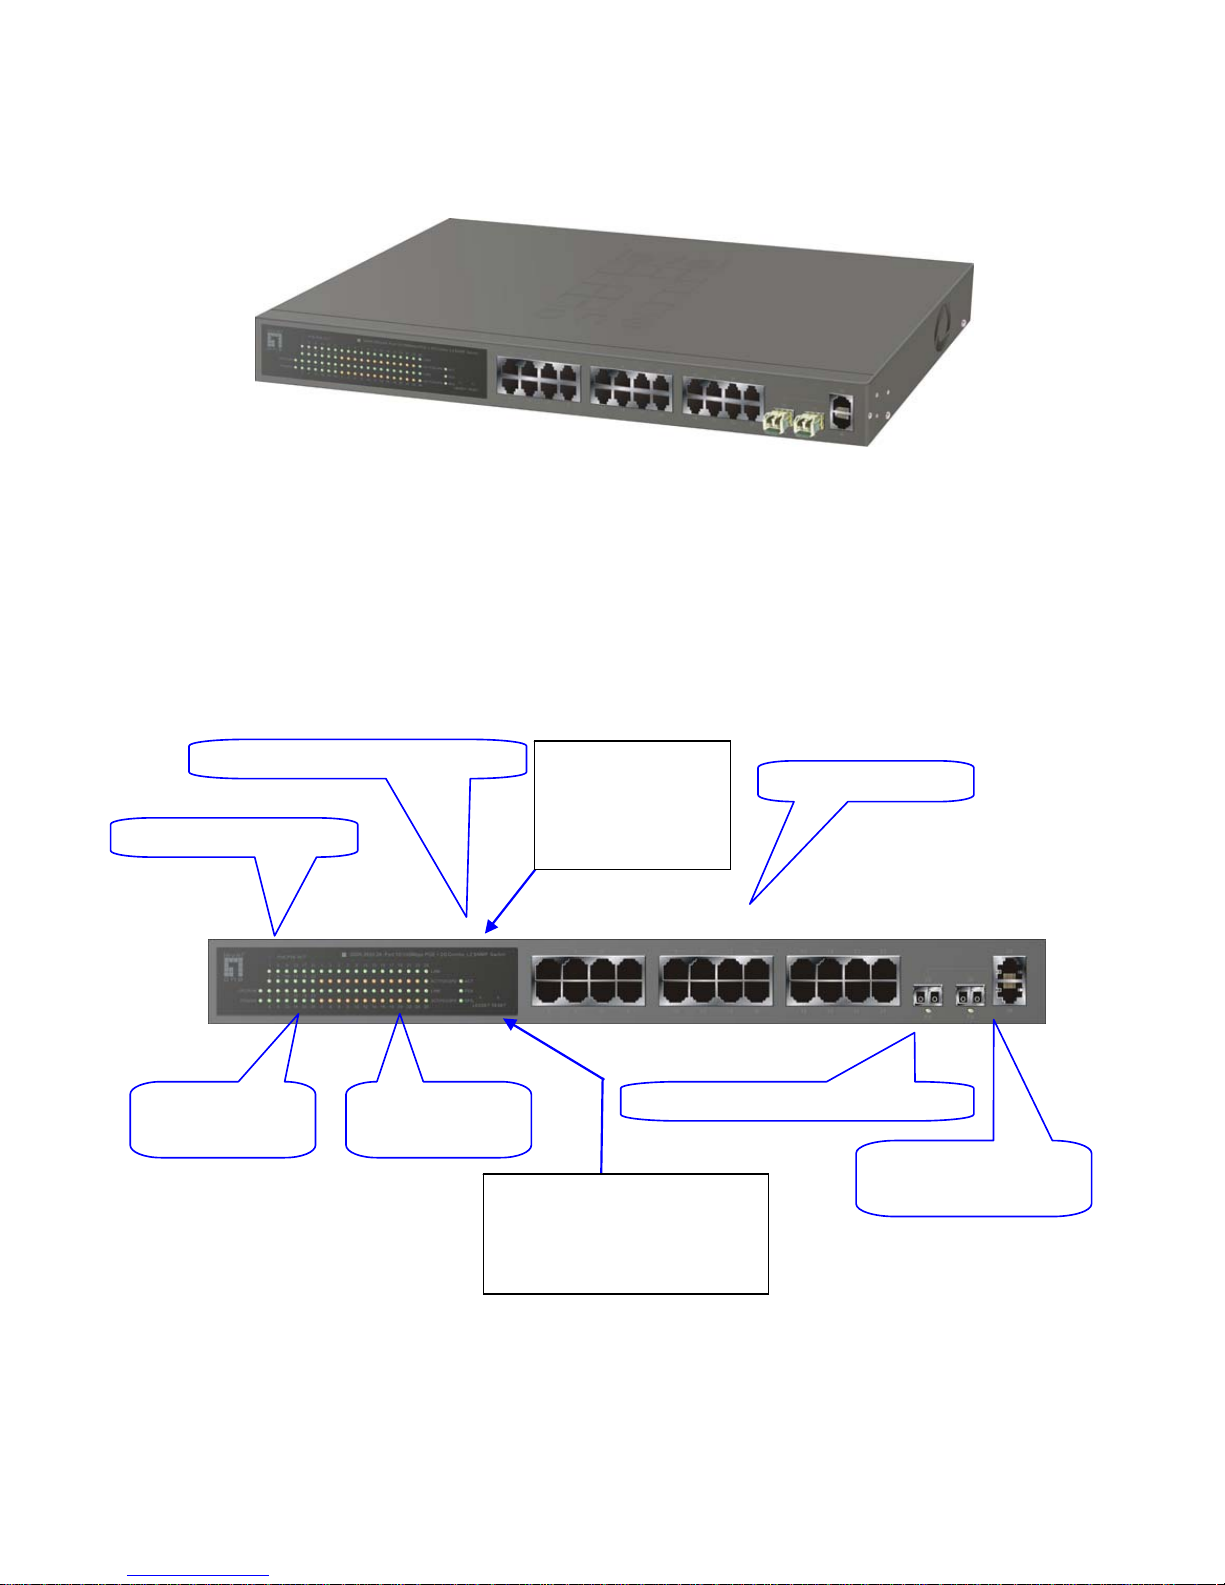
There are 24 TP Fast Ethernet ports and 2 slots for optional removable
modules on the front panel of the switch. LED display area, locating on the front
panel, contains a CPURUN, Power LED and 26 ports working status of the switch.
Fig. 1-1 Full View
Fig. 1-2 Front View of the GSW-2693
Power Indication LED
Fast Ethernet Port
LED SET Mode: ACT/FDX/SPD
Gigabit Dual Media
Port(25~26): SFP/TP
LEDSET Button
LEDSET button is
used to change
the LED display
mode
PoE Port Status
Indication LEDs
Fiber Port Status Indication LEDs
TP Port Status
Indication LEDs
RESET Button:
RESET button is used to
reset the management
system.
Page 14
6
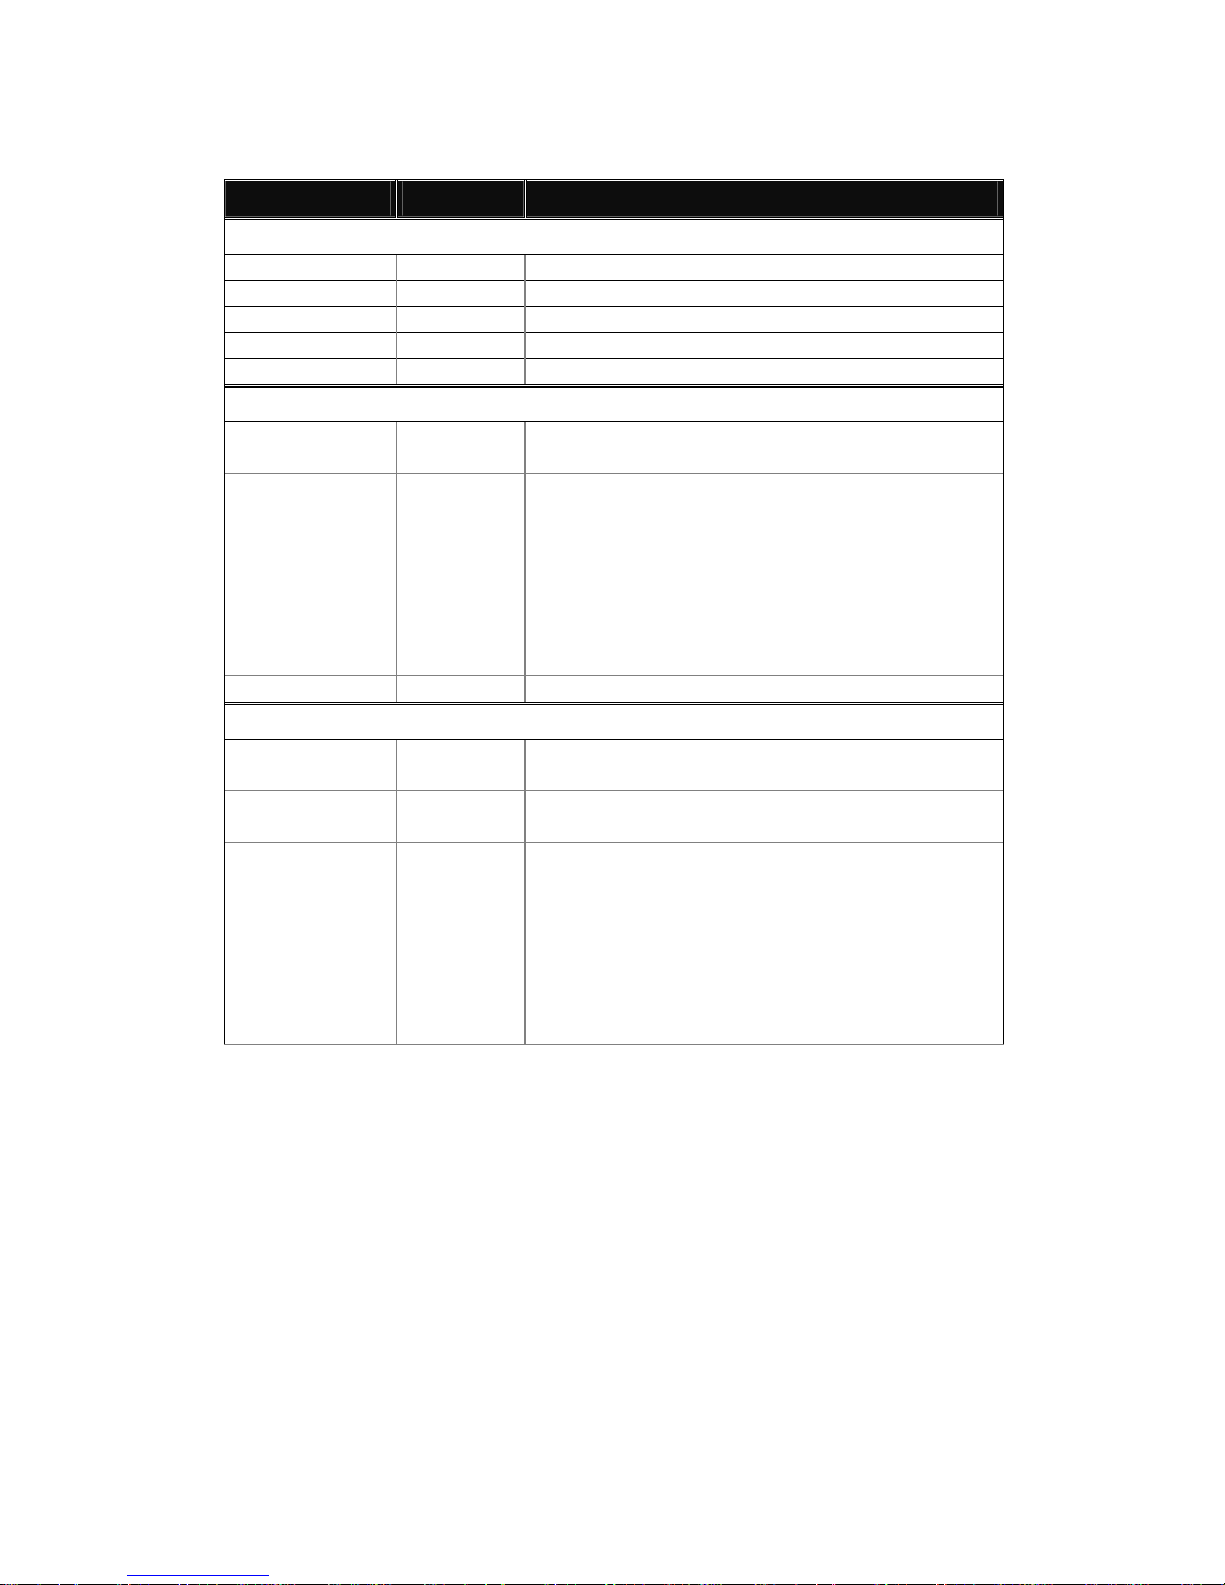
• LED Indicators
LED Color Function
System LED
CPURUN Green Lit when CPU is on and good
POWER Green Lit when AC power is on and good
ACT Green Lit when LEDSET set on active mode
FDX Green Lit when LEDSET set on full-duplex mode
SPD Green Lit when LEDSET set on speed mode
10/100Mbps Ethernet TP Port 1 to 24 LED
LINK Green
Lit when connection with remote device is good
Off when cable connection is not good
ACT/FDX/ SPD
Amber
(TP Port 1
to 24 LED)
a. LEDSET set on ACT (active) mode:
Blinks when any traffic is present
b. LEDSET set on FDX (full-duplex) mode:
Lit when full-duplex mode is active
Blinks when any collision is present
c. LEDSET set on SPD (speed) mode:
Lit when 100Mbps speed is active
Off when 10Mbps speed is active
PoE-PSE ACT Green Lit when PoE Power is active
10/100/1000Mbps Gigabit TP/Fiber Port 25, 26 LED
LINK Green
Lit when connection with remote device is good
Off when cable connection is not good
FX Green
Lit when Fiber port is active
Off when TP port is a ctive
ACT/FDX/ SPD
Green
(Port 25,
26 LED)
a. LEDSET set on ACT (active) mode:
Blinks when any traffic is present
b. LEDSET set on FDX (full-duplex) mode:
Lit when full-duplex mode is active
Blinks when any collision is present
c. LEDSET set on SPD (speed) mode:
Lit when 1000Mbps speed is active
Off when 10/100Mbps speed is active
Table1-1
Page 15
7
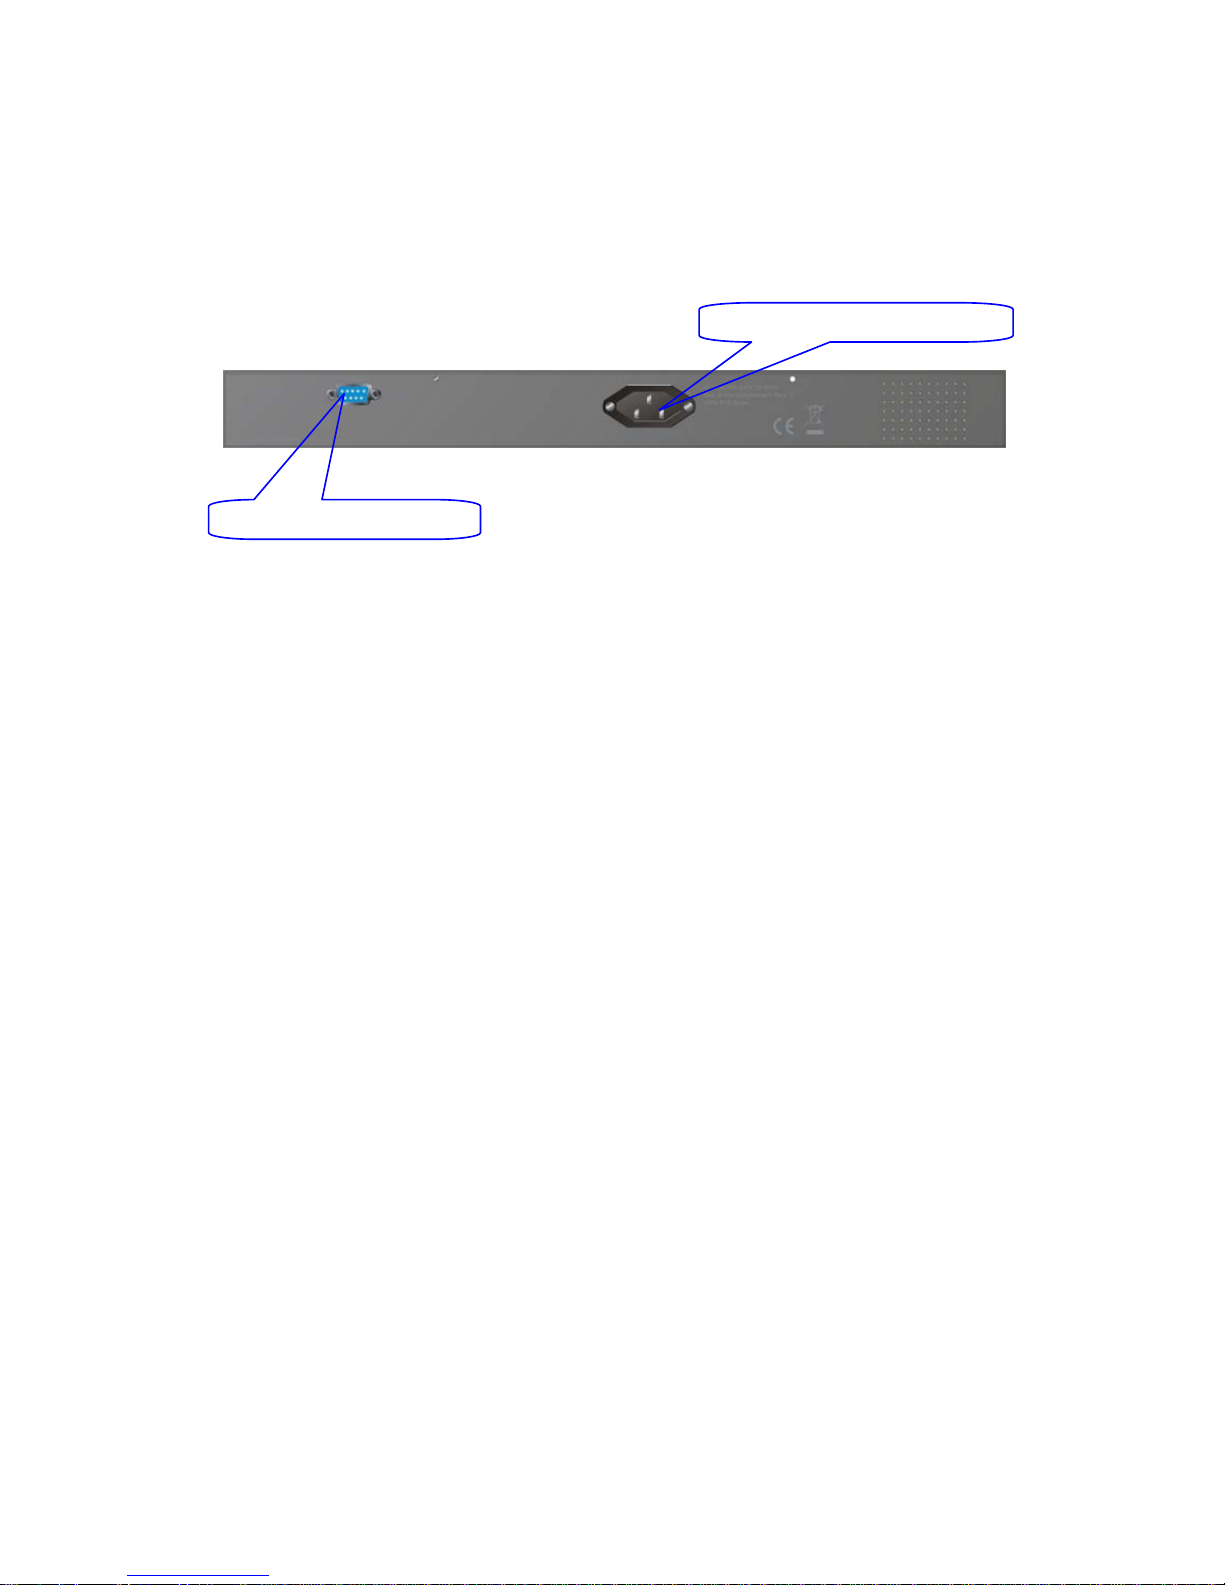
1-4-2. Rear Panel
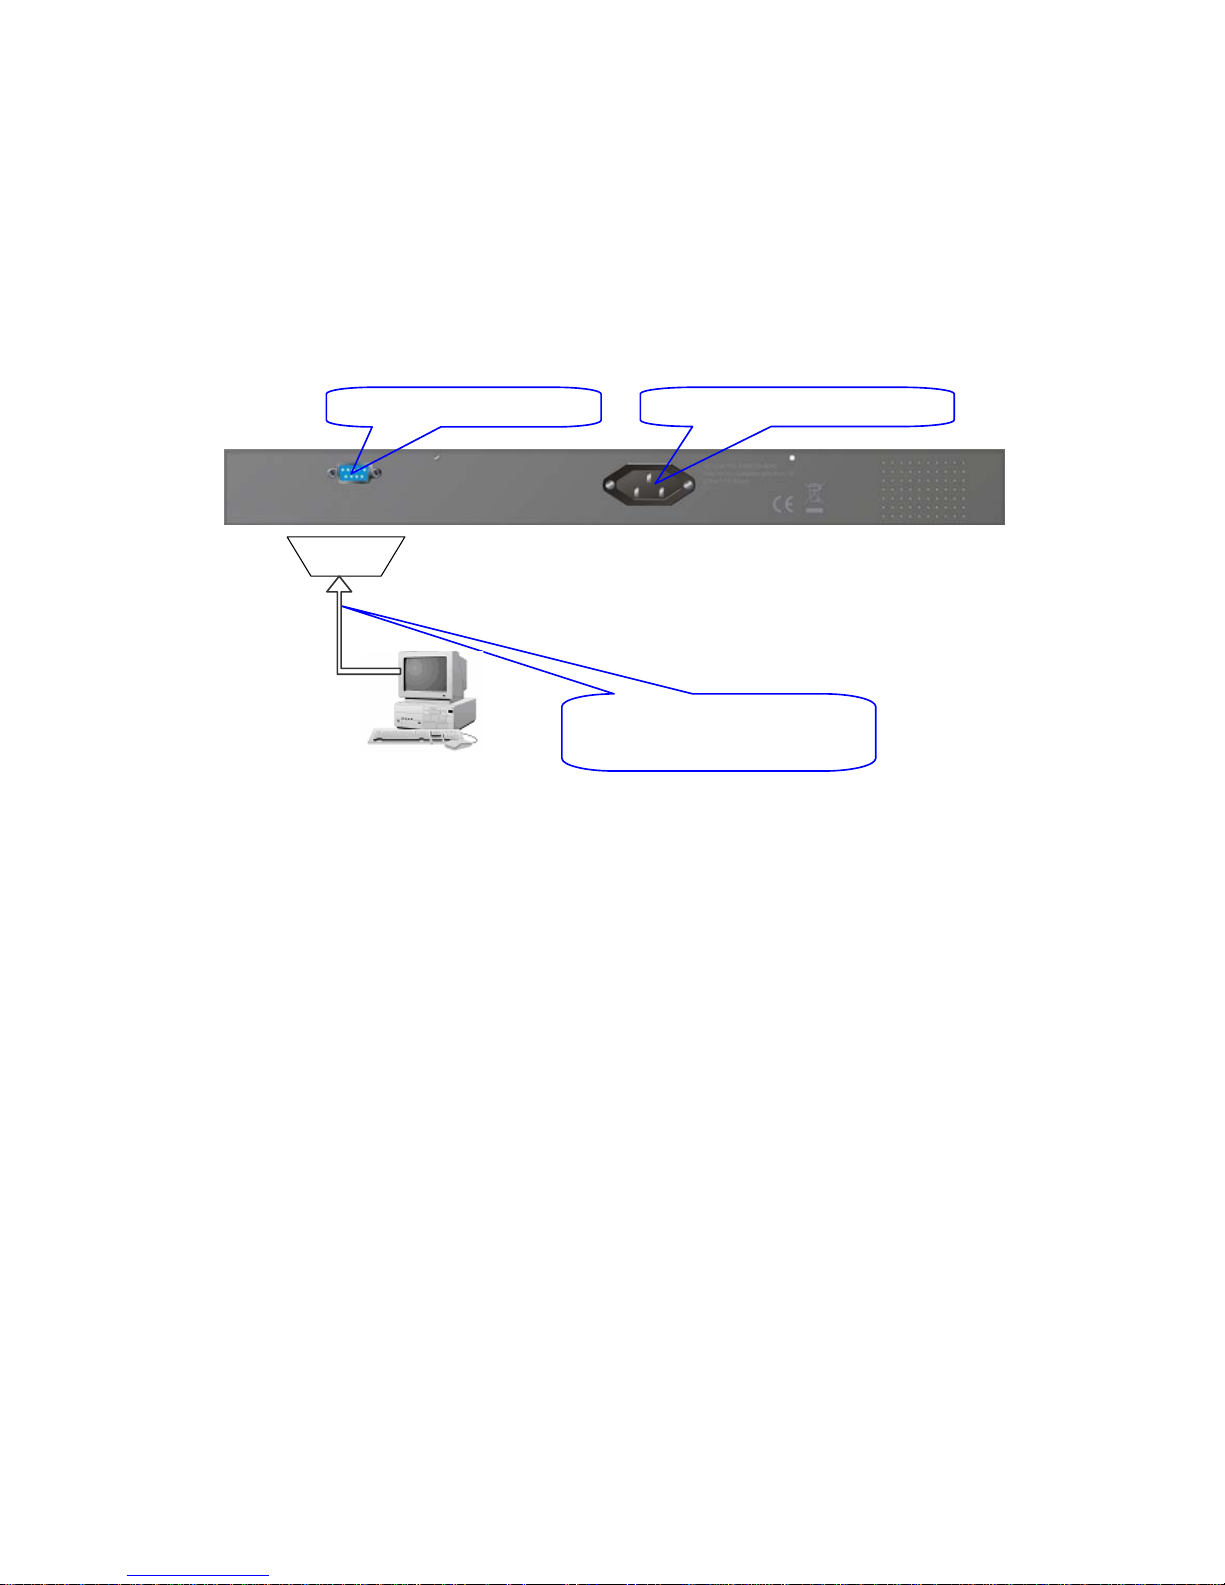
One RS-232 DB-9 interface is offered for configuration or management. And
there is one AC power input socket for having the switch powered on or off.
Fig. 1-3 Rear View of the GSW-2693
RS-232 DB-9 Connector
AC Line 100-240V 50/60 Hz
Page 16
8
1-5. Optional Modules
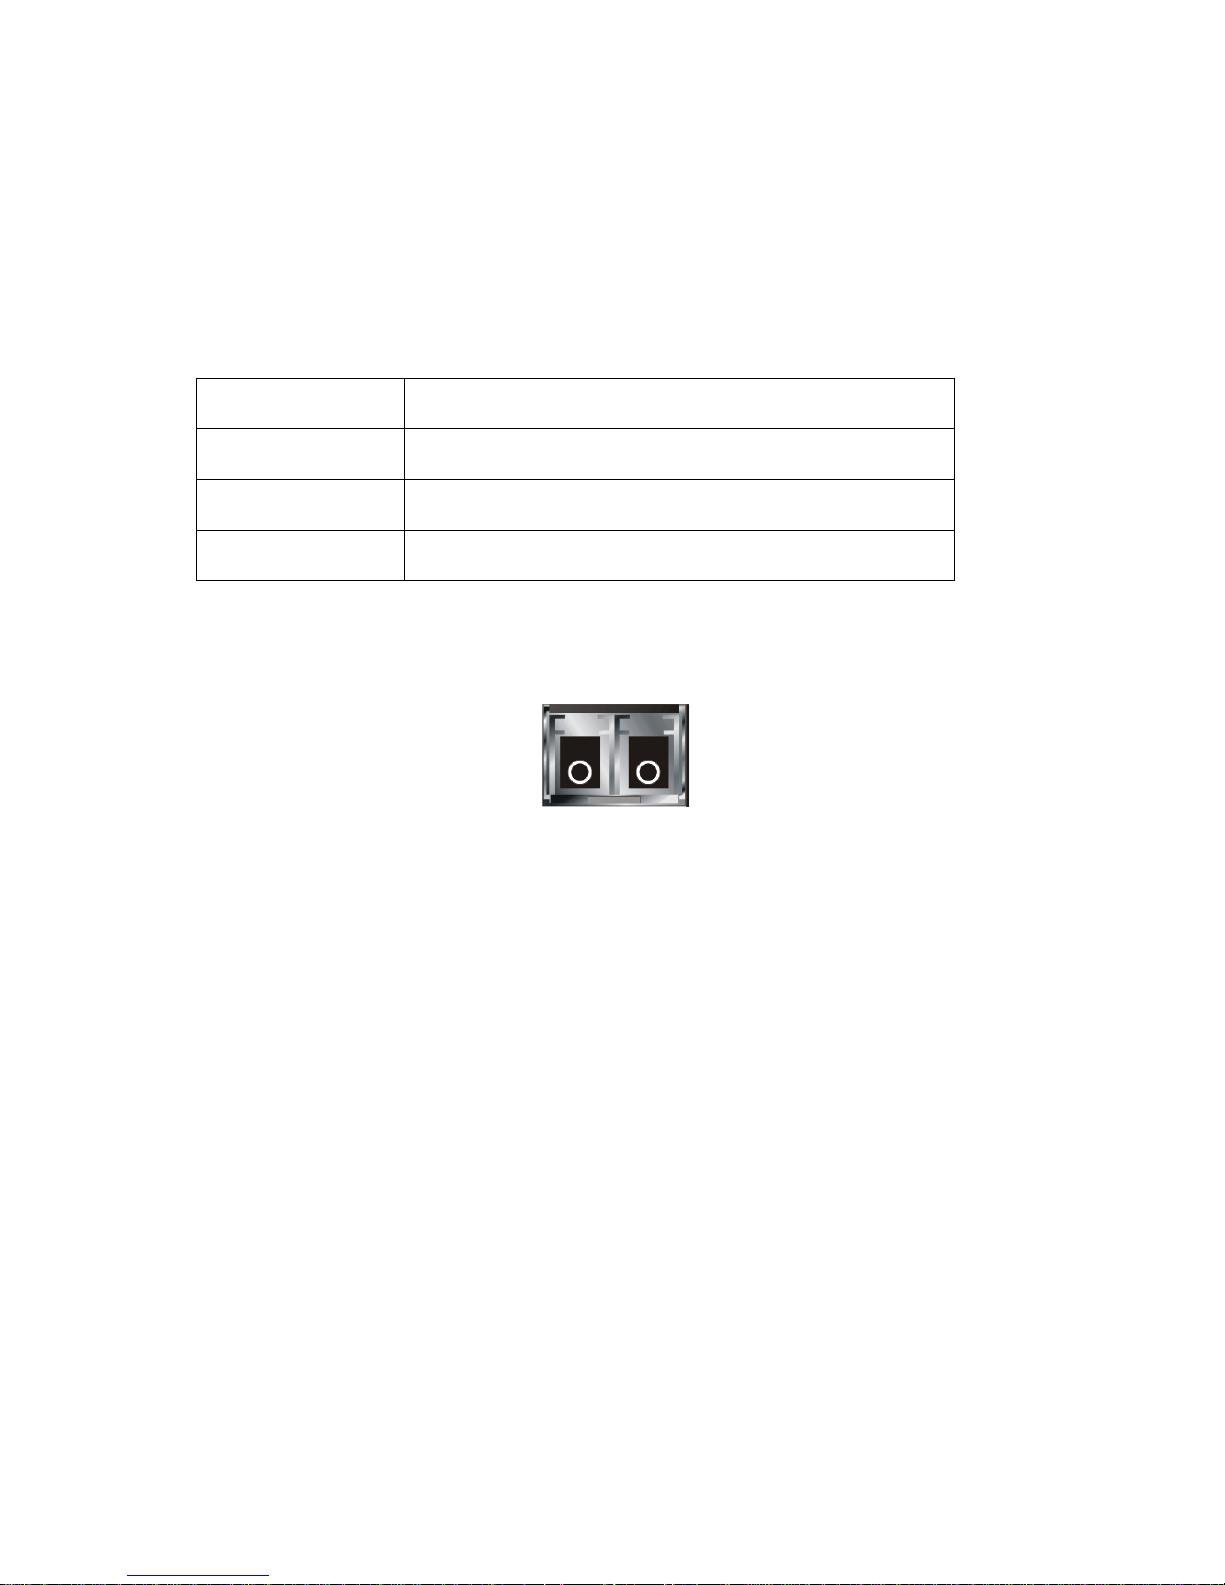
In the switch, Port 25, 26 includes two types of media --- TP and SFP Fiber
this port supports 10/100/1000Mbps TP or 1000Mbps SFP Fiber with auto-detected
function. 1000Mbps SFP Fiber transceiver is used for high-speed connection
expansion; the following are optional SFP types provided for the switch:
Model No. Description
GVT-0300 Multi-mode SFP Transceiver, 550m
GVT-0301 Single-mode SFP Transceiver, 10Km
GVT-0302 Single-mode SFP Transceiver, 70Km
Fig. 1-4 Front View of 1000Base-SX/LX LC, SFP Fiber Transceiver
Page 17
9
2. Installation
2-1. Starting Up
This section will give users a quick start for:
- Hardware and Cable Installation
- Management Station Installation
- Software booting and configuration
2-1-1. Hardware and Cable Installation
At the beginning, please do first:
⇒ Wear a grounding device to avoid the damage from electrostatic discharge
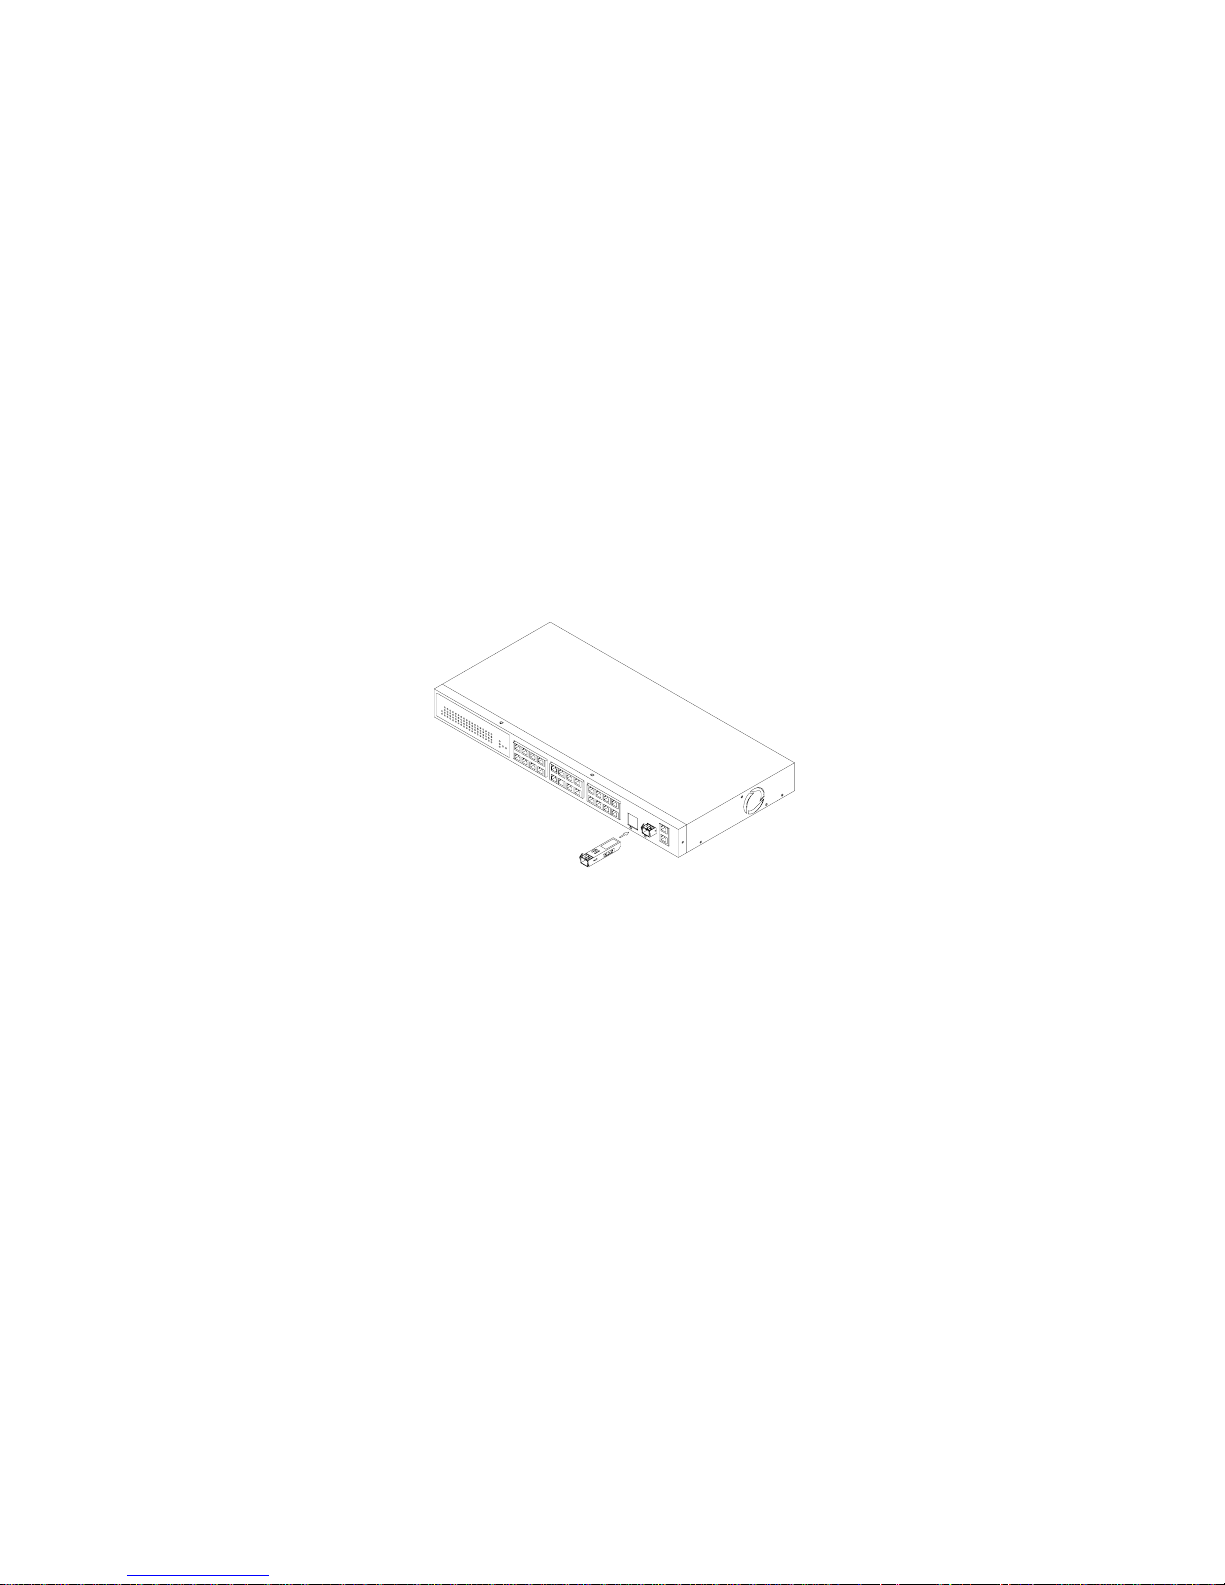
• Installing Optional SFP Fiber Transceivers to the GSW-2693 Switch
Note: If you have no modules, please skip this section.
• Connecting the SFP Module to the Chassis:
The optional SFP modules are hot swappable, so you can plug or unplug it
before or after powering on.
1. Verify that the SFP module is the right model and conforms to the
chassis
2. Slide the module along the slot. Also be sure that the module is properly
seated against the slot socket/connector
3. Install the media cable for network connection
4. Repeat the above steps, as needed, for each module to be installed into
slot(s)
5. Have the power ON after the above procedures are done
Fig. 2-1 Installation of Optional SFP Fiber Transceive
r
Page 18
10
• TP Port and Cable Installation
⇒ In the switch, TP port supports MDI/MDI-X auto-crossover, so both types of
cable, straight-through (Cable pin-outs for RJ-45 jack 1, 2, 3, 6 to 1, 2, 3, 6 in
10/100M TP; 1, 2, 3, 4, 5, 6, 7, 8 to 1, 2, 3, 4, 5, 6, 7, 8 in Gigabit TP) and
crossed-over (Cable p in-outs for R J-45 jack 1, 2, 3, 6 to 3, 6, 1, 2) can be used.
It means you do not have to tell from them, just plug it.
⇒ Use Cat. 5 grade RJ-45 TP cable to connect to a TP port of the switch and the
other end is connected to a network-aware device such as a workstation or a
server.
⇒ Repeat the above steps, as needed, for each RJ-45 port to be connected to a
Gigabit 10/100/1000 TP device.
Now, you can start having the switch in operation.
• Power On
The switch supports 100-240 VAC, 50-60 Hz power supply. The power
supply will automatically convert the local AC power source to DC power. It does not
matter whether any connection plugged into the switch or not when power on, even
modules as well. After the power is on, all LED indicators will light up immediately
and then all off except the power LED still keeps on. This represents a reset of the
system.
• Firmware Loading
After resetting, the bootloader will load the firmware into the memory. It will
take about 30 seconds, after that, the switch will flash all the LED once and
automatically performs self-test and is in ready state.
Page 19
11
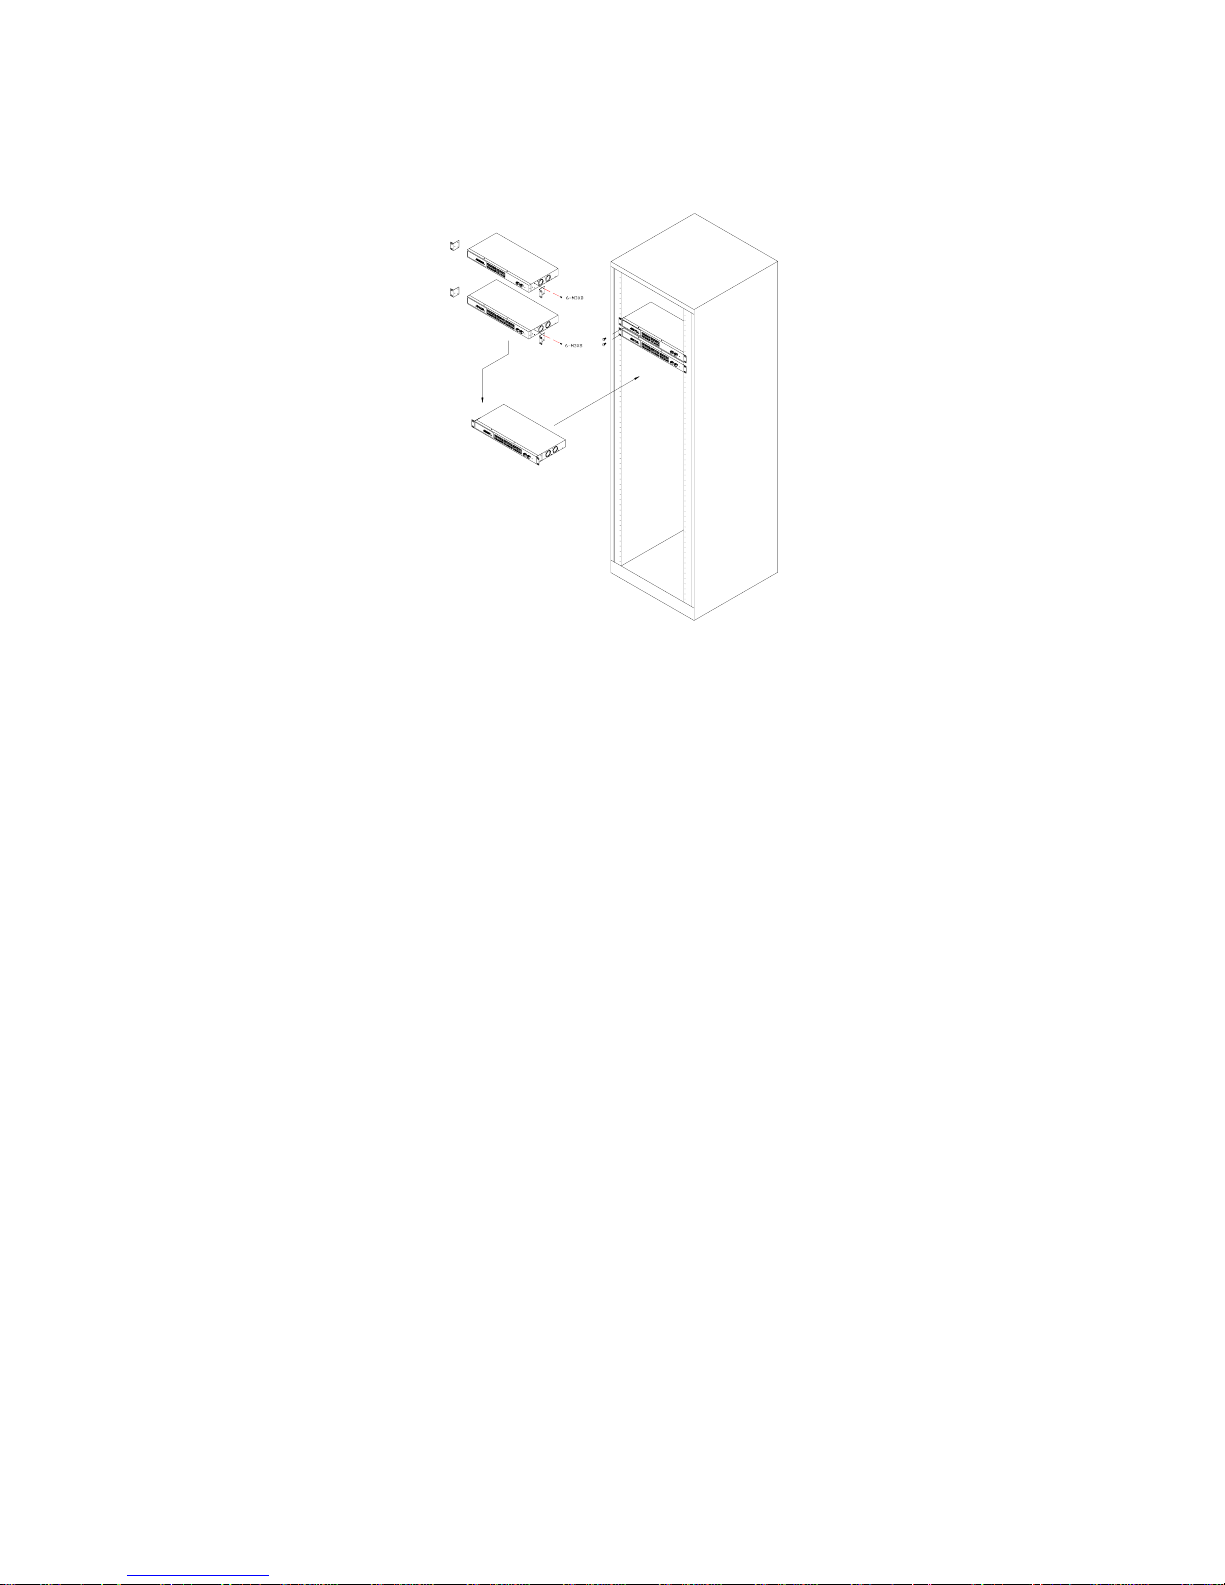
2-1-2. 19-Inch Wiring Closet Rail
Caution: Allow a proper spacing and proper air ventilation for the cooling fan
at both sides of the chassis.
⇒ Wear a grounding device for electrostatic discharge.
⇒ Screw the mounting accessory to the front side of the switch (See Fig. 2-2).
⇒ Place the Chassis into the 19-inch wiring closet rail and locate it at the proper
position. Then, fix the Chassis by screwing it.
2-1-3. Cabling Requirements
To help ensure a successful installation and keep the network performance
good, please take a care on the cabling requirement. Cables with worse
specification will render the LAN to work poorly.
Fig. 2-2
Page 20
12
2-1-3-1. Cabling Requirements for TP Ports
⇒ For Fast Ethernet TP network connection
⎯ The grade of the cable must be Cat. 5 or Cat. 5e with a maximum length of
100 meters.
⇒ Gigabit Ethernet TP network connection
⎯ The grade of the cable must be Cat. 5 or Cat. 5e with a maximum length of
100 meters. Cat. 5e is recommended.
2-1-3-2. Cabling Requirements for 1000SX/LX SFP Module
It is more complex and comprehensive contrast to TP cabling in the fiber
media. Basically, there are two categories of fiber, multi mode (MM) and single
mode (SM). The later is categorized into several classes by the distance it supports.
They are SX, LX, LHX, XD, and ZX. From the viewpoint of connector type, there
mainly are LC and BiDi-SC.
⎯ Gigabit Fiber with multi-mode LC SFP module
⎯ Gigabit Fiber with single-mode LC SFP module
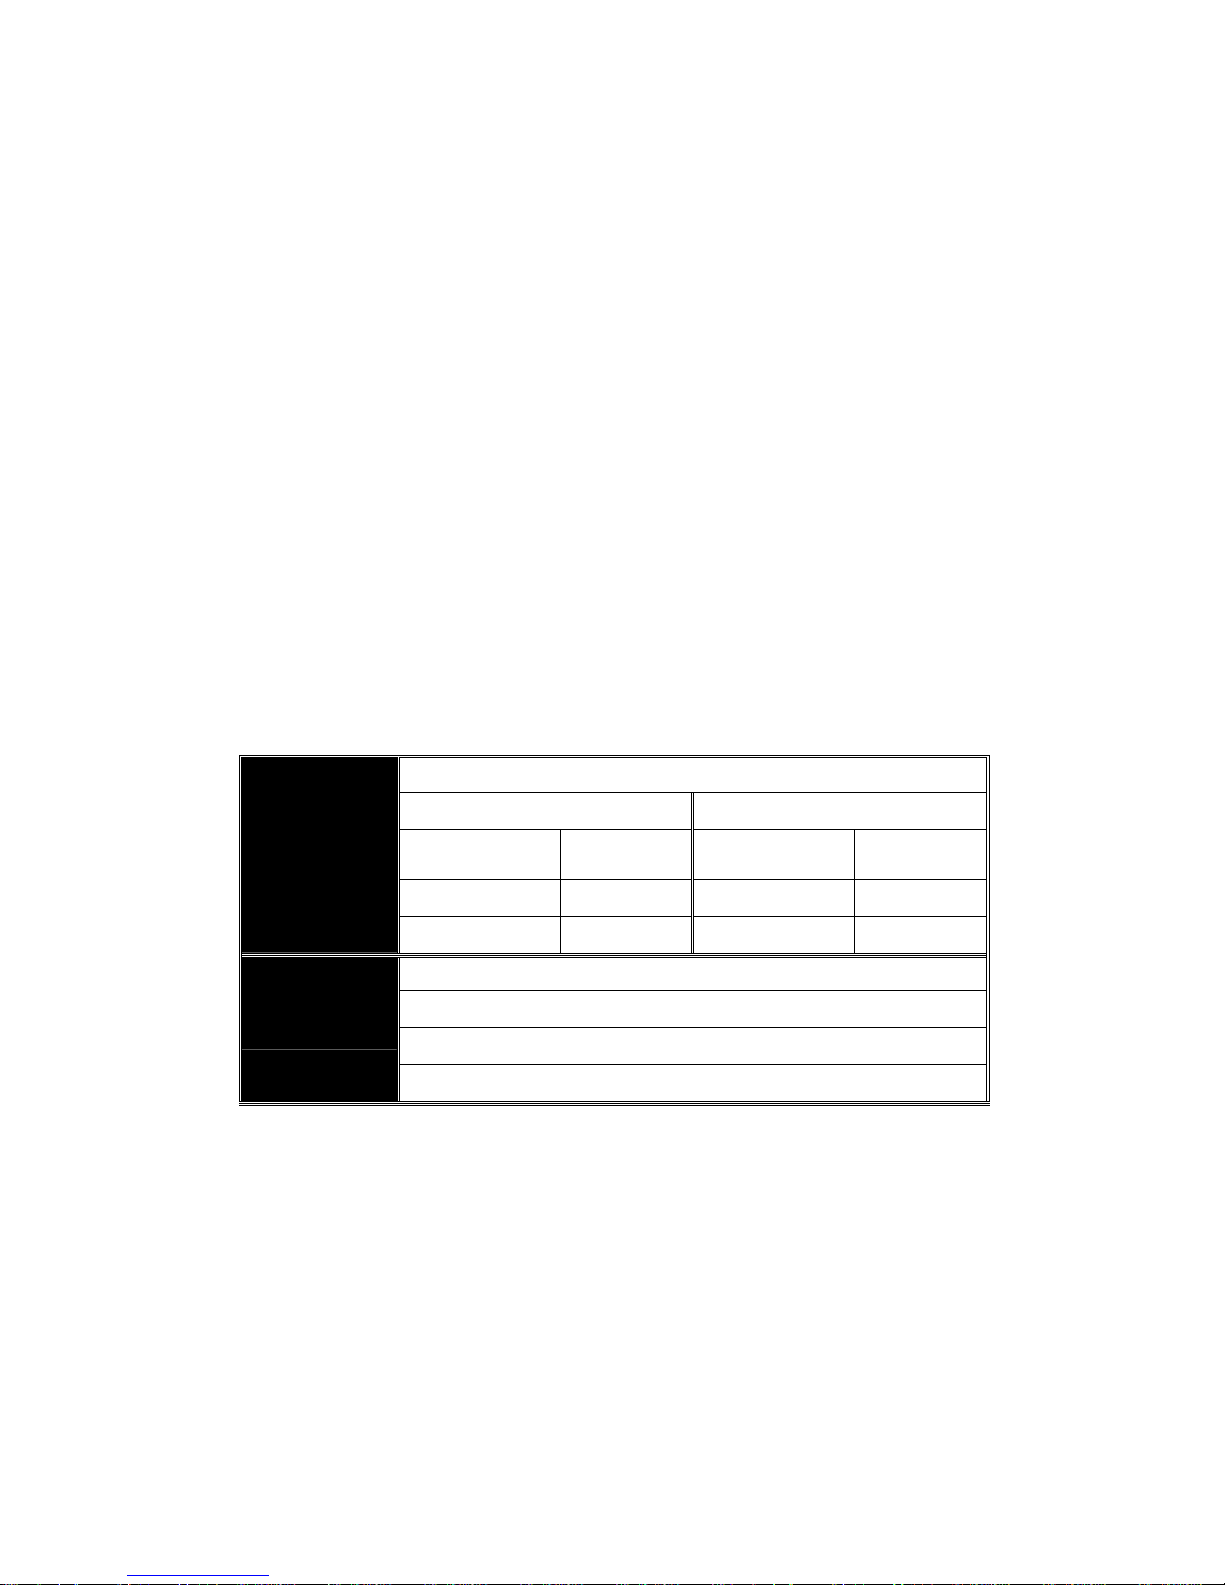
The following table lists the types of fiber that we support and those else not
listed here are available upon request.
Multi-mode Fiber Cable and Modal Bandwidth
Multi-mode 62.5/125μm Multi-mode 50/125μm
Modal
Bandwidth
Distance
Modal
Bandwidth
Distance
160MHz-Km 220m 400MHz-Km 500m
IEEE 802.3z
Gigabit Ethernet
1000SX 850nm
200MHz-Km 275m 500MHz-Km 550m
GVT-0301 10Km, GVT-0302 70 Km
Single-mode Fiber 9/125μm
Single-mode transceiver 1310nm 10Km
1000BaseLX/LHX/XD/ZX
Single-mode transceiver 1550nm 70Km
Table2-1
Page 21
13
2-1-3-3. Switch Cascading in Topology
• Takes the Delay Time into Account
Theoretically, the switch partitions the collision domain for each port in switch
cascading that you may up-link the switches unlimitedly. In practice, the network
extension (cascading levels & overall diameter) must follow the constraint of the
IEEE 802.3/802.3u/802.3z and other 802.1 series protocol specifications, in which
the limitations are the timing requirement from physical signals defined by 802.3
series specification of Media Access Control (MAC) and PHY, and timer from some
OSI layer 2 protocols such as 802.1d, 802.1q, LACP and so on.
The fiber, TP cables and devices’ bit-time delay (round trip) are as follows:
1000Base-X TP, Fiber 100Base-TX TP 100Base-FX Fiber
Round trip Delay: 4096 Round trip Delay: 512
Cat. 5 TP Wire: 11.12/m Cat. 5 TP Wire: 1.12/m Fiber Cable: 1.0/m
Fiber Cable : 10.10/m TP to fiber Converter: 56
Bit Time unit : 1ns (1sec./1000 Mega bit)
Bit Time unit: 0.01μs (1sec./100 Mega bit)
Table 2-2
Sum up all elements’ bit-time delay and the overall bit-time delay of
wires/devices must be within Round Trip Delay (bit times) in a half-duplex network
segment (collision domain). For full-duplex operation, this will not be applied. You
may use the TP-Fiber module to extend the TP node distance over fiber optic and
provide the long haul connection.
• Typical Network Topology in Deployment
A hierarchical network with minimum levels of switch may reduce the timing
delay between server and client station. Basically, with this approach, it will
minimize the number of switches in any one path; will lower the possibility of
network loop and will improve network efficiency. If more than two switches are
connected in the same network, select one switch as Level 1 switch and connect all
other switches to it at Level 2. Server/Host is recommended to connect to the Level
1 switch. This is general if no VLAN or other special requirements are applied.
Page 22
14
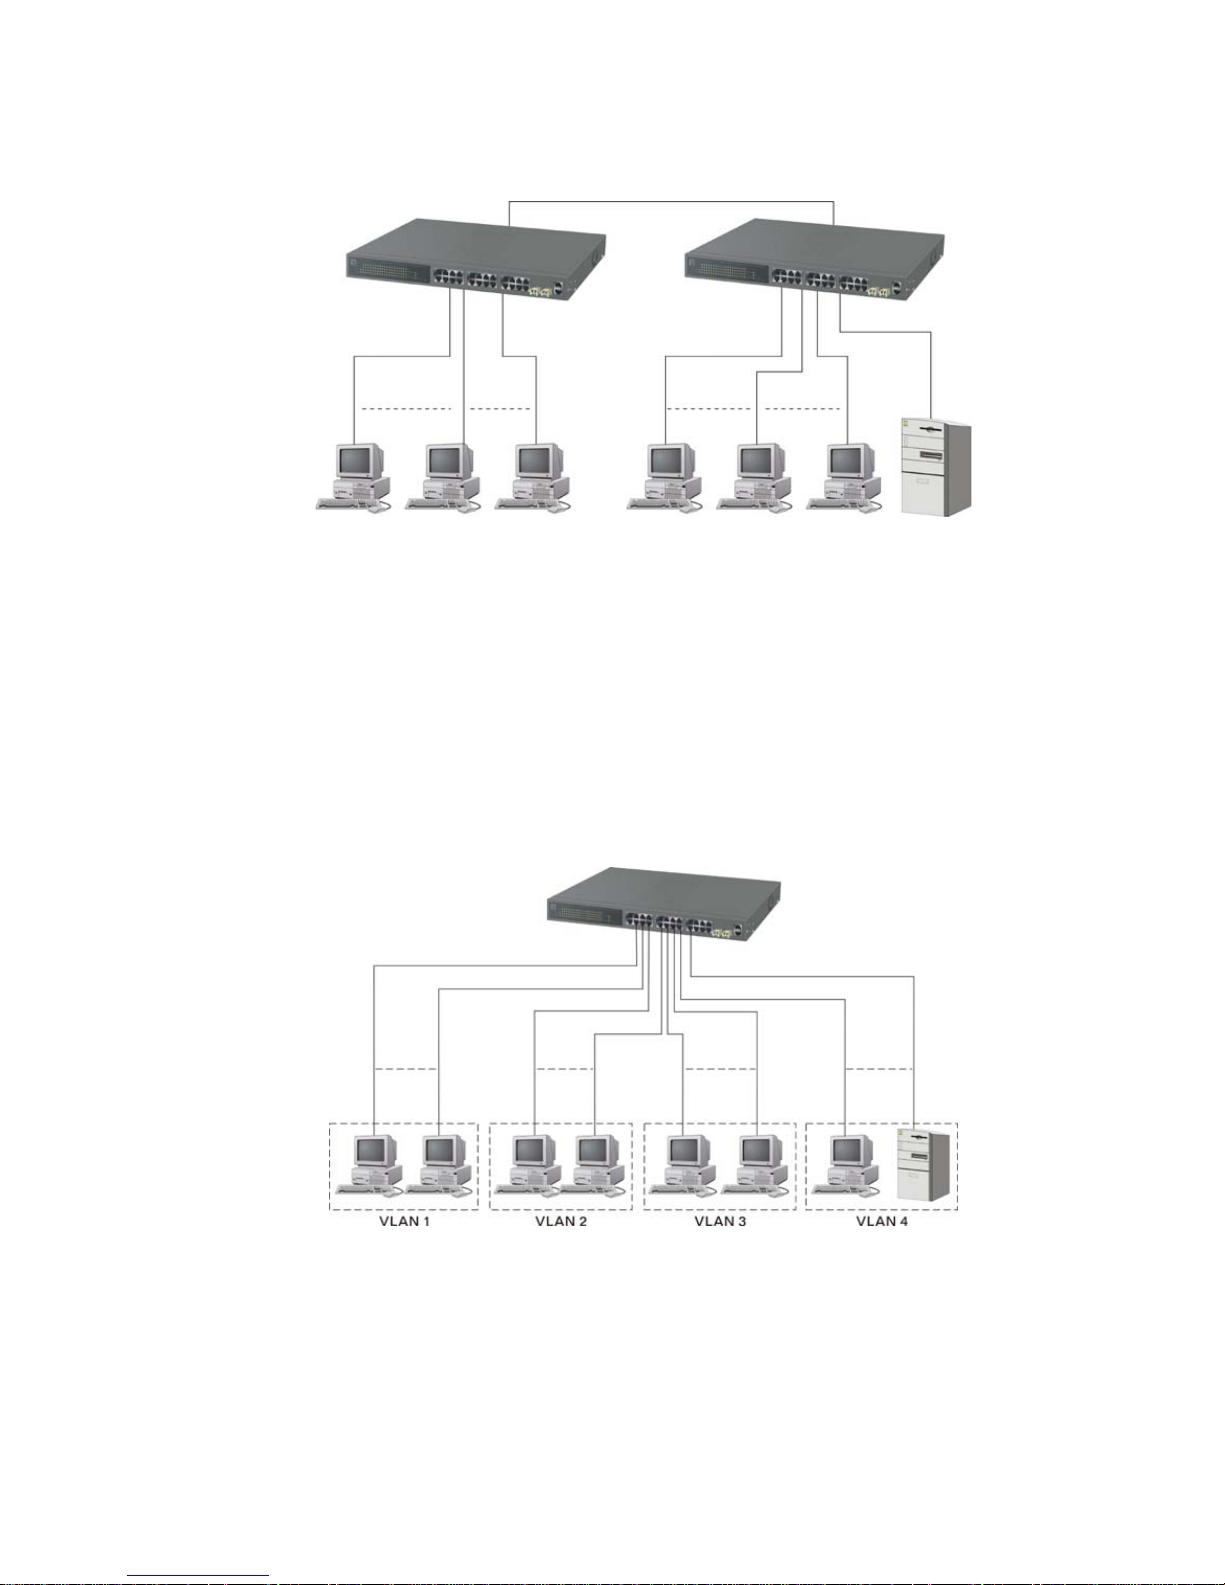
Case1: All switch ports are in the same local area network. Every port can access
each other (See Fig. 2-3).
If VLAN is enabled and configured, each node in the network that can
communicate each other directly is bounded in the same VLAN area.
Here VLAN area is defined by what VLAN you are using. The switch
supports both port-based VLAN and tag-based VLAN. They are different in practical
deployment, especially in physical location. The following diagram shows how it
works and what the difference they are.
Case2a: Port-based VLAN (See Fig.2-4).
1. The same VLAN members could not be in dif f erent switches.
2. Every VLAN members could not access VLAN members each other.
3. The switch manager has to assign dif ferent names for each VLAN groups
at one switch.
Fig. 2-3 No VLAN Configuration Diagram
Fig. 2-4 Port-based VLAN Diagram
Page 23
15
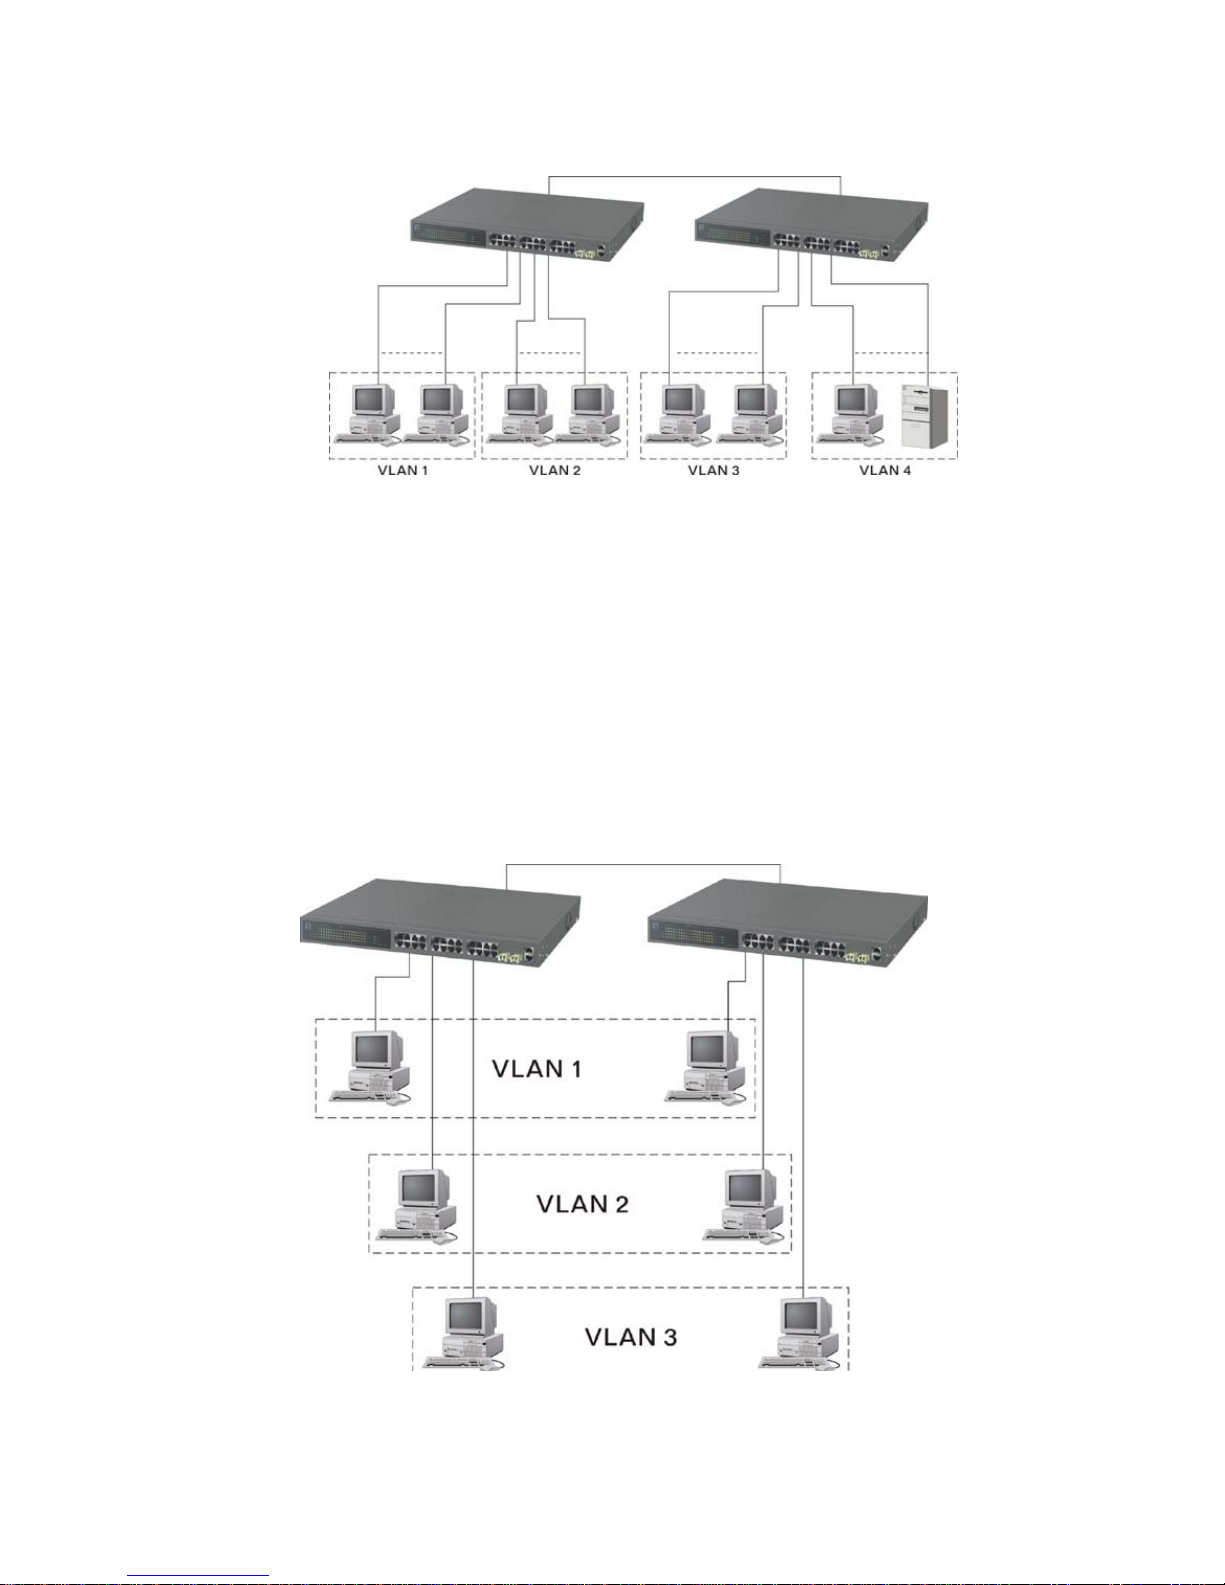
Case 2b: Port-based VLAN (See Fig.2-5).
1. VLAN1 members could not access VLAN2, VLAN3 and VLAN4 members.
2. VLAN2 members could not access VLAN1 and VLAN3 members, but they could
access VLAN4 members.
3. VLAN3 members could not access VLAN1, VLAN2 and VLAN4.
4. VLAN4 members could not access VLAN1 and VLAN3 members, but they could
access VLAN2 members.
Case3a: The same VLAN members can be at different switches with the same VID
(See Fig. 2-6).
Fig. 2-5 Port-based VLAN Diagram
Fig. 2-6 Attribute-based VLAN Diagram
Page 24
16
2-1-4. Configuring the Management Agent
We offer you three ways to startup the switch management function. They
are RS-232 console, CLI, and Web. Users can use any one of them to monitor and
configure the switch. You can touch them through the following procedures.
Section 2-1-4-1: Configuring the Management Agent of GSW-2693 through the
Serial RS-232 Port
Section 2-1-4-2: Configuring the Management Agent of GSW-2693 through the
Ethernet Port
Note: Please first modify the IP address, Subnet mask, Default gateway and DNS
through RS-232 console, and then do the next.
Page 25
17
2-1-4-1. Configuring the Management Agent of GSW-2693 through the Serial
RS-232 Port
To perform the configuration through RS-232 console port, the switch’s serial
port must be directly connected to a DCE device, for example, a PC, through
RS-232 cable with DB-9 connector. Next, run a terminal emulator with the default
setting of the switch’s serial port. With this, you can communicate with the switch.
In the switch, RS-232 interface only supports baud rate 57.6k bps with 8 data
bits, 1 stop bit, no parity check and no flow control.
To configure the switch, please follow the procedures below:
1. Find the RS-232 DB-9 cable with female DB-9 connector bundled.
Normally, it just uses pins 2, 3 and 7. See also Appendix B for more
details on Null Modem Cable Specifications.
2. Attaches the DB-9 female cable connector to the male serial RS-232
DB-9 connector on the switch.
3. Attaches the other end of the serial RS-232 DB-9 cable to PC’ s serial
port, running a terminal emulator supporting VT100/ANSI terminal with
The switch’s serial port default settings. For example,
Windows98/2000/XP HyperTerminal utility.
Note: The switch’s serial port default settings are listed as follows:
Baud rate 57600
Stop bits 1
Data bits 8
Parity N
Flow control none
4. When you complete the connection, then press <Enter> key. The login
prompt will be shown on the screen. The default username and
password are shown as below:
Username = admin Password = admin
GSW-2693
Default IP Setting:
IP address = 192.168.1.1
Subnet Mask = 255.255.255.0
Default Gateway = 192.168.1.254
Terminal or Terminal Emulator
Fig. 2-7
RS-232 cable with female
DB-9 connector at both ends
RS-232
AC Line 100-240V 50/60 Hz RS-232 DB-9 Connector
Page 26
18
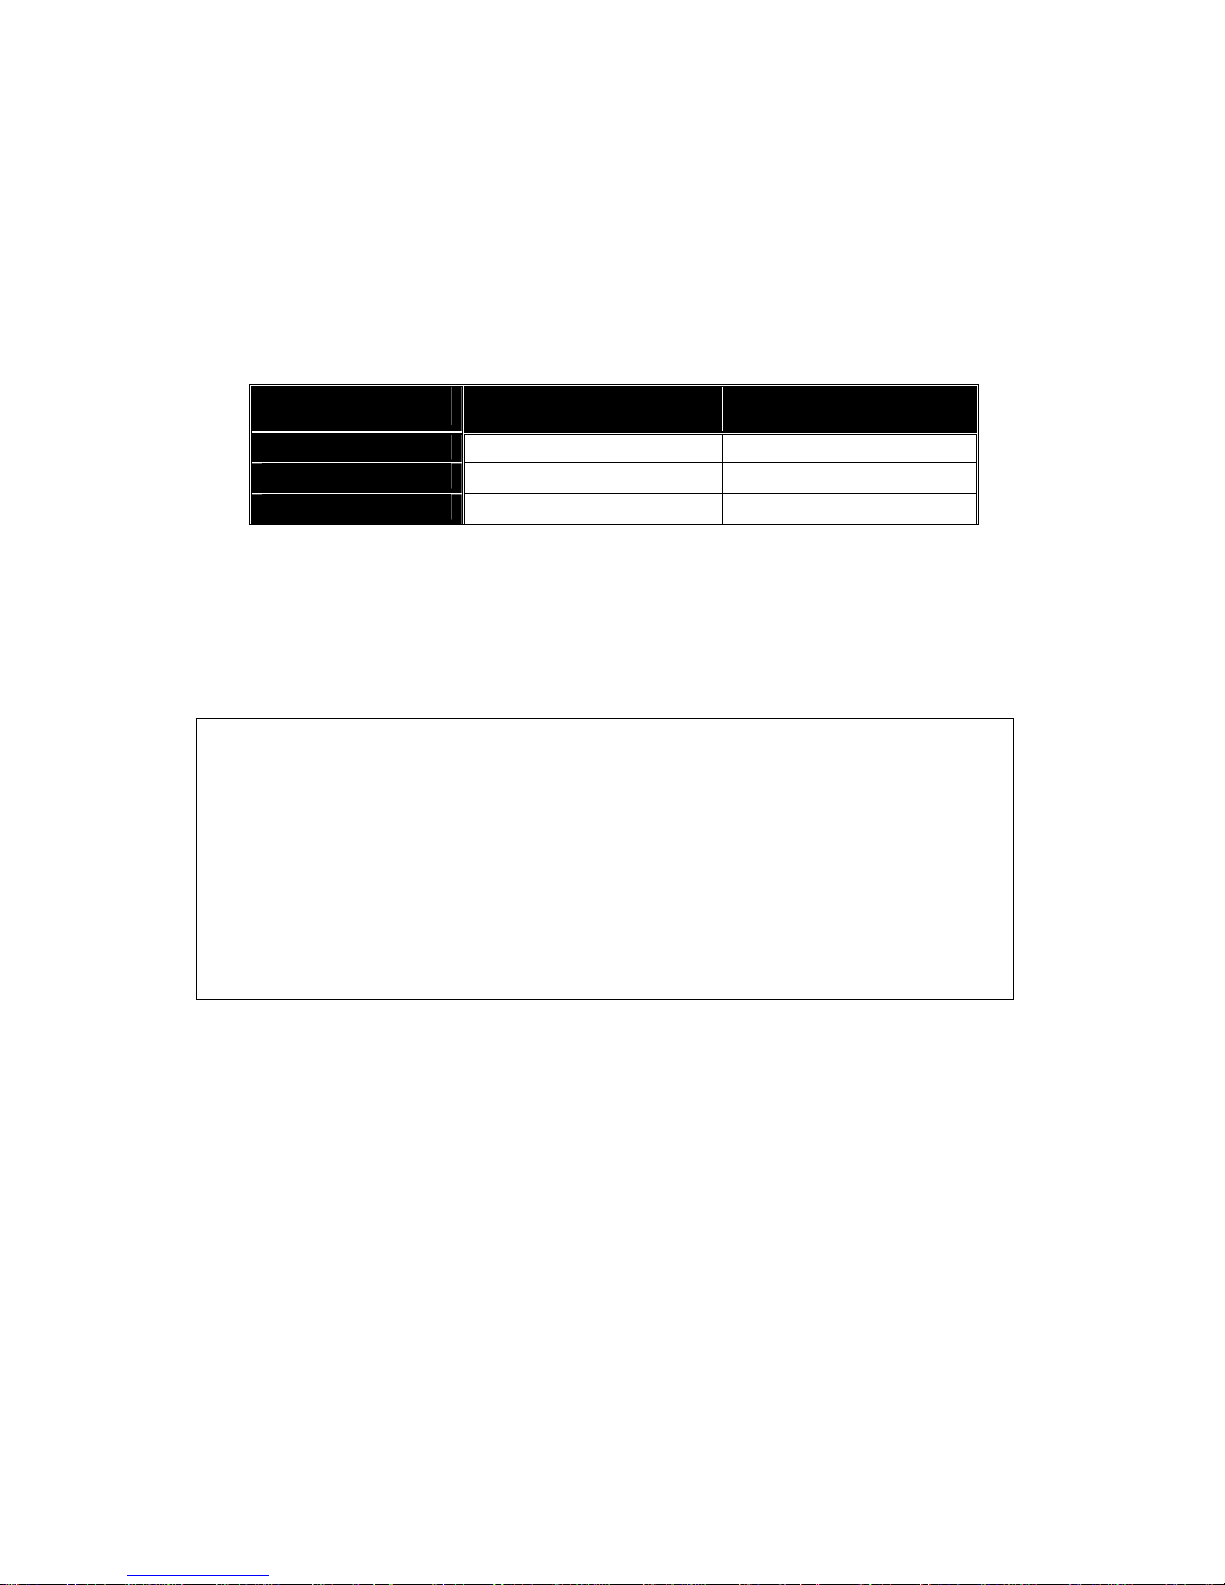
• Set IP Address, Subnet Mask and Default Gateway IP Address
Please refer to Fig. 2-7 CLI Management for details. They are default setting
of IP address. You can first either configure your PC IP address or change IP
address of the switch, next to change the IP address of default gateway and subnet
mask.
For example, your network address is 10.1.1.0, and subnet mask is
255.255.255.0. You can change the switch’s default IP address 19 2.168.1.1 to
10.1.1.1 and set the subnet mask to be 255.255.255.0. Then, choo se your default
gateway, may be it is 10.1.1.254.
Default Value GSW-2693 Your Network Setting
IP Address
192.168.1.1 10.1.1.1
Subnet
255.255.255.0 255.255.255.0
Default Gateway
192.168.1.254 10.1.1.254
Table 2-3
After completing these settings in the switch, it will reboot to have the
configuration taken effect. After this step, you can operate the management through
the network, no matter it is from a web browser or Network Management System
(NMS).
Managed Switch – GSW-2693
Login: admin
Password:
GSW-2693#
Fig. 2-8 the Login Screen for CLI
Page 27
19
2-1-4-2. Configuring the Management Agent of GSW-2693 through the
Ethernet Port
There are three ways to configure and monitor the switch through the
switch’s Ethernet port. They are CLI, Web browser and SNMP manager. The user
interface for the last one is NMS dependent and does not cover here. We just
introduce the first two types of management interface.
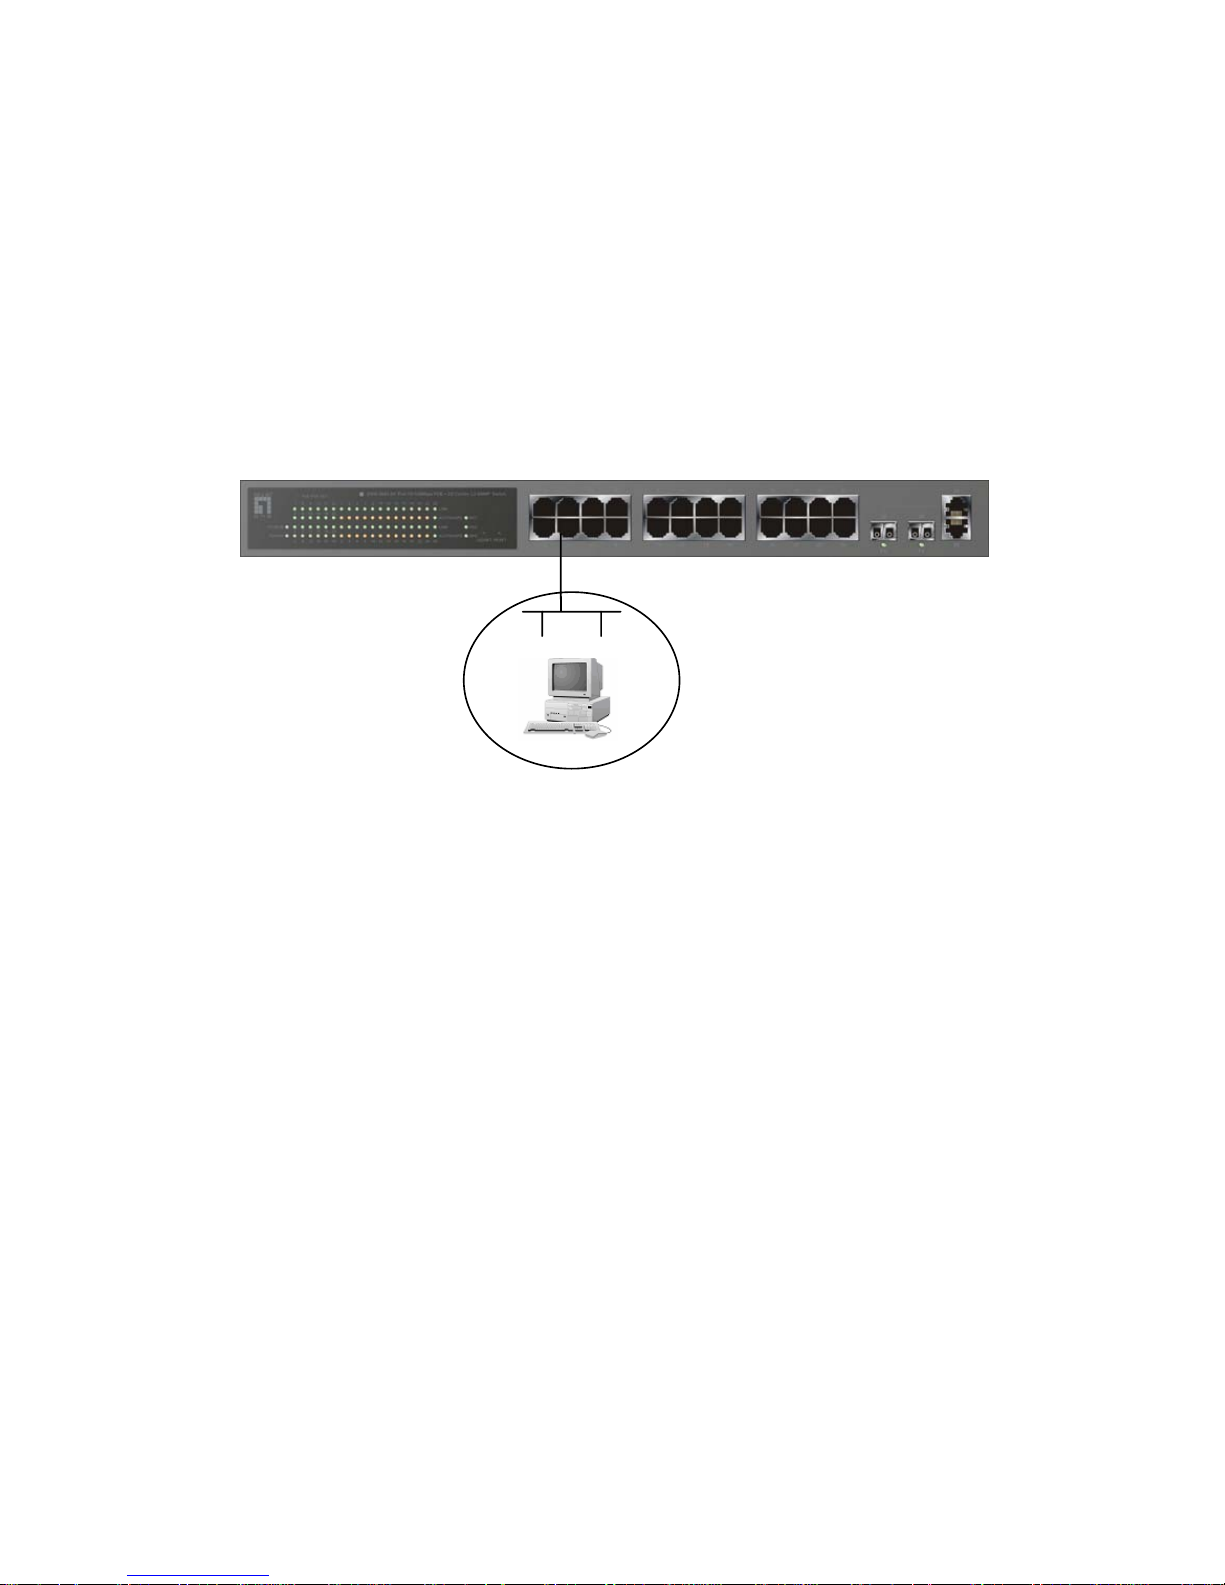
• Managing GSW-2693 through Ethernet Port
Before you communicate with the switch, you have to finish first the
configuration of the IP address or to know the IP address of the switch. Then,
follow the procedures listed below.
1. Set up a physical path between the configured the switch and a PC by a
qualified UTP Cat. 5 cable with RJ-45 connector.
Note: If PC directly connects to the switch, you have to setup the same
subnet mask between them. But, subnet mask may be different for the PC
in the remote site. Please refer to Fig. 2-9 about the switch’s default IP
address information.
2. Run CLI or web browser and follow the menu. Please refer to Chapter 3
and Chapter 4.
GSW-2693
Default IP Setting:
IP = 192.168.1.1
Subnet Mask = 255.255.255.0
Default Gateway = 192.168.1.254
Assign a reasonable IP address,
For example:
IP = 192.168.1.100
Subnet Mask = 255.255.255.0
Default Gateway = 192.168.1.254
Fig. 2-9
Ethernet LAN
Page 28
20
Fig. 2-10 the Login Screen for Web
2-1-5. IP Address Assignment
For IP address configuration, there are three parameters needed to be filled
in. They are IP address, Subnet Mask, Default Gate way and DNS.
IP address:
The address of the network device in the network is used for internetworking
communication. Its address structure looks is shown in the Fig. 2-11. It is “classful”
because it is split into predefined address classes or categories.
Each class has its own network range between the network identifier and
host identifier in the 32 bits address. Each IP address comprises two parts: network
identifier (address) and host identifier (address). The former indicates the network
where the addressed host resides, and the latter indicates the individual host in the
network which the address of host refers to. And the host identifier must be unique
in the same LAN. Here the term of IP address we used is version 4, known as IPv4.
Network identifier Host identifier
Fig. 2-11 IP address structure
32 bits
Page 29
21
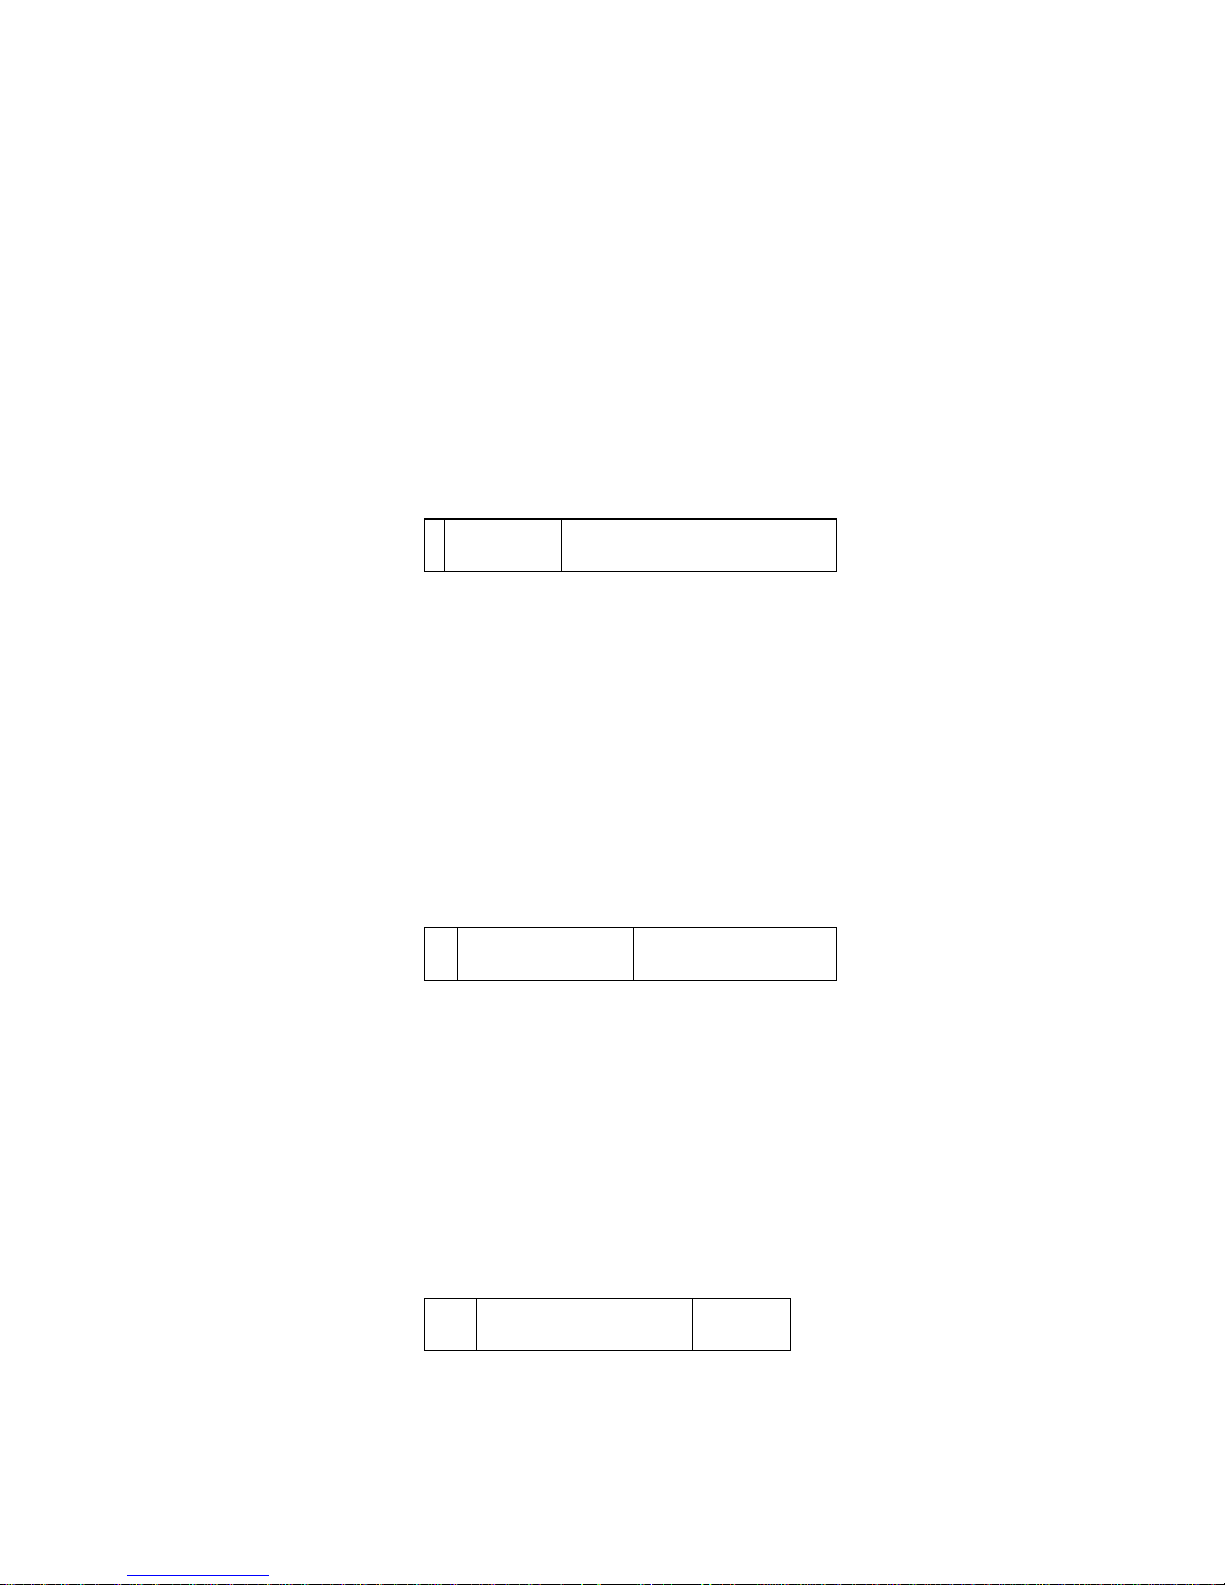
With the classful addressing, it divides IP address into three classes, class A,
class B and class C. The rest of IP addresses are for multicast and broadcast. The
bit length of the network prefix is the same as that of the subnet mask and is
denoted as IP address/X, for example, 192.168.1.0/24. Each class has its address
range described below.
Class A:
Address is less than 126.255.255.255. There are a total of 126 networks can
be defined because the address 0.0.0.0 is reserved for default route and
127.0.0.0/8 is reserved for loopback function.
0
Class B:
IP address range between 128.0.0.0 and 191.255.255.255. Each class B
network has a 16-bit network prefix followed 16-bit host address. There are 16,384
(2^14)/16 networks able to be defined with a maximum of 65534 (2^16 –2) hosts
per network.
10
Class C:
IP address range between 192.0.0.0 and 223.255.255.255. Each class C
network has a 24-bit network prefix followed 8-bit host address. There are
2,097,152 (2^21)/24 networks able to be defined with a maximum of 254 (2^8 –2)
hosts per network.
110
Bit # 0 1 7 8
Network address Host address
Bit # 01 2 15 16
Network address Host address
Bit # 0 1 2 3 23 24 31
Network address Host
Page 30
22
Class D and E:
Class D is a class with first 4 MSB (Most significance bit) set to 1-1-1-0 and
is used for IP Multicast. See also RFC 1112. Class E is a class with first 4 MSB set
to 1-1-1-1 and is used for IP broadcast.
According to IANA (Internet Assigned Numbers Authority), there are three
specific IP address blocks reserved and able to be used for extending internal
network. We call it Private IP address a nd list below:
Class A 10.0.0.0 --- 10.255.255.255
Class B 172.16.0.0 --- 172.31.255.255
Class C 192.168.0.0 --- 192.168.2 55.255
Please refer to RFC 1597 and RFC 1466 for more information.
Subnet mask:
It means the sub-division of a class-based network or a CIDR block. The
subnet is used to determine how to split an IP address to the network prefix and the
host address in bitwise basis. It is designed to utilize IP address more efficiently and
ease to manage IP network.
For a class B network, 128.1.2.3, it may have a subnet mask 255.255.0.0 in
default, in which the first two bytes is with all 1s. This means more than 60
thousands of nodes in flat IP address will be at the same network. It’s too large to
manage practically. Now if we divide it in to smaller network by extending network
prefix from 16 bits to, say 24 bits, that’s using its third byte to subnet this class B
network. Now it has a subnet mask 255.255.255.0, in which each bit of the first
three bytes is 1. It’s now clear that the first two bytes is used to identify the class B
network, the third byte is used to identify the subnet within this class B network and,
of course, the last byte is the host number.
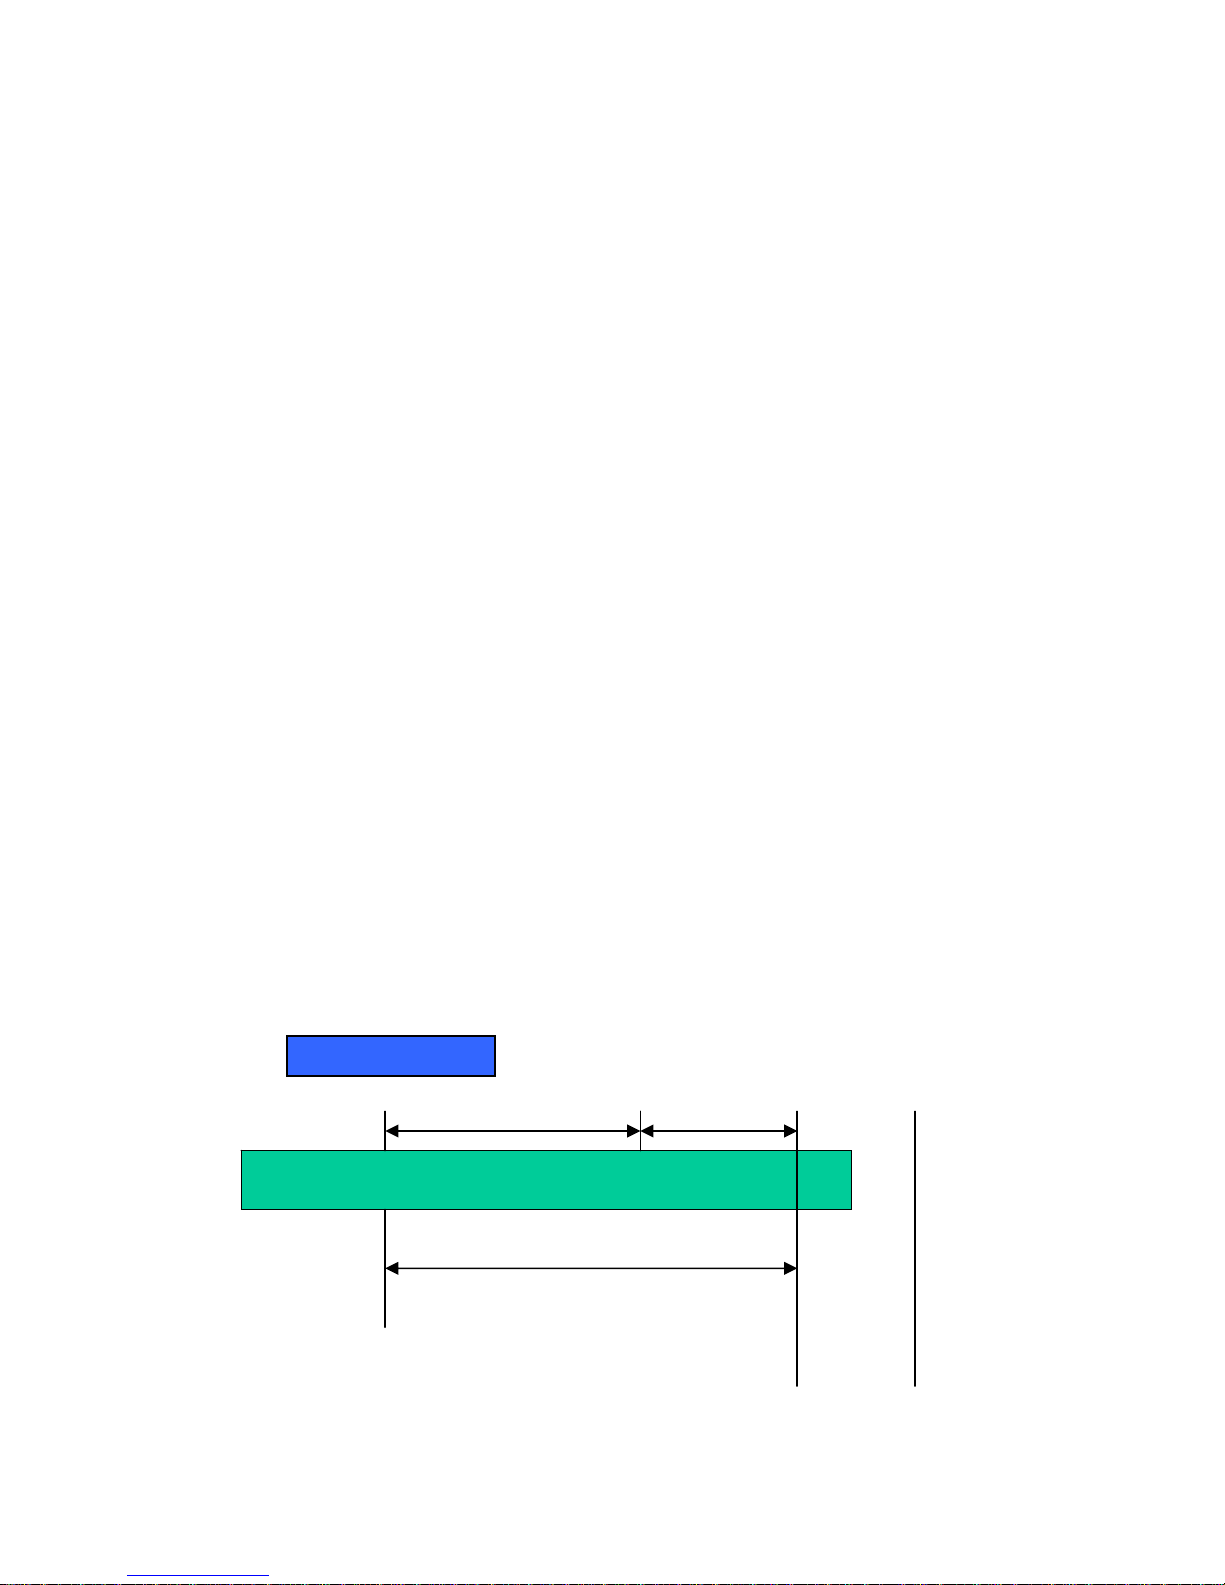
Not all IP address is available in the sub-netted network. Two special
addresses are reserved. They are the addresses with all zero’s and all one’s host
number. For example, an IP address 128.1.2.128, what IP address reserved will be
looked like? All 0s mean the network itself, and all 1s mean IP broadcast.
10000000.00000001.00000010.1 0000000
25 bits
1 0000000
1 1111111
All 0s = 128.1.2.128
All 1s= 128.1.2.255
SubneNetwork
Page 31
23
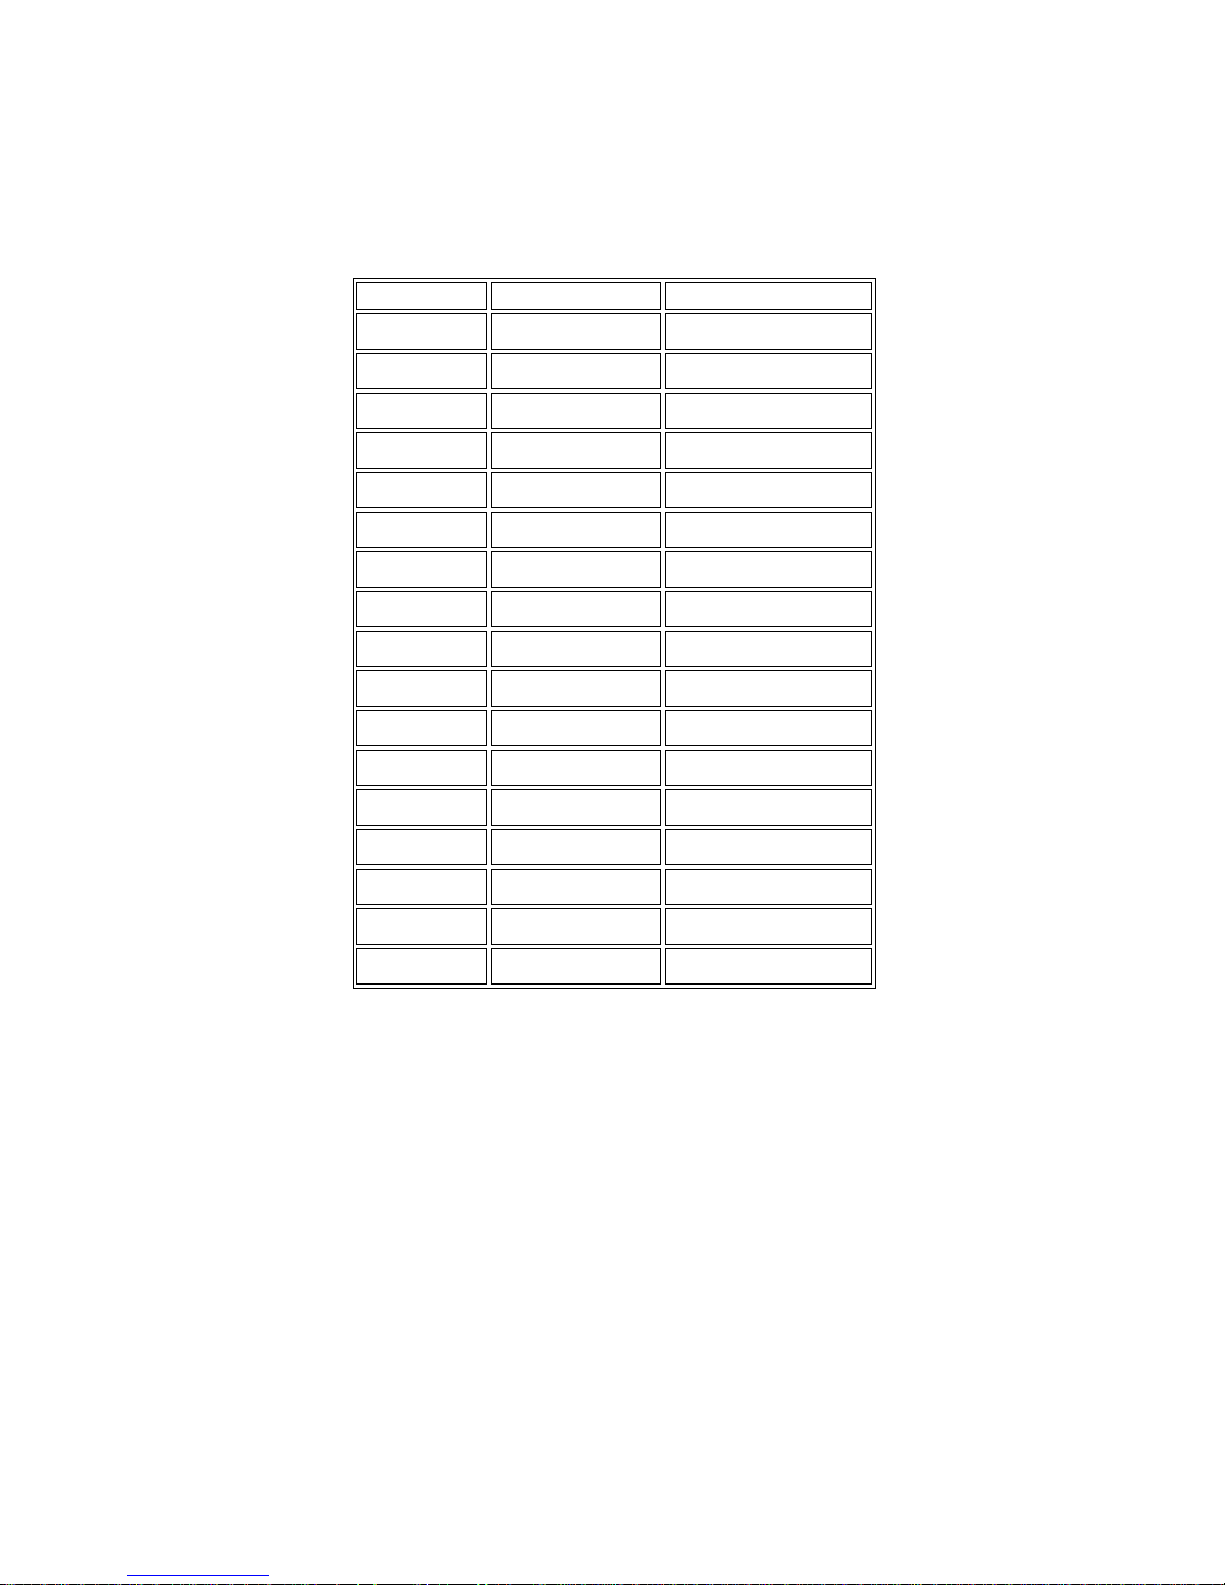
In this diagram, you can see the subnet mask with 25-bit long,
255.255.255.128, contains 126 members in the sub-netted network. Another is that
the length of network prefix equals the number of the bit with 1s in that subnet mask.
With this, you can easily count the number of IP addresses matched. The following
table shows the result.
Prefix Length No. of IP matched No. of Addressable IP
/32 1 /31 2 /30 4 2
/29 8 6
/28 16 14
/27 32 30
/26 64 62
/25 128 126
/24 256 254
/23 512 510
/22 1024 1022
/21 2048 2046
/20 4096 4094
/19 8192 8190
/18 16384 16382
/17 32768 32766
/16 65536 65534
Table 2-4
According to the scheme above, a subnet mask 255.255.255.0 will partition a
network with the class C. It means there will have a maximum of 254 effective
nodes existed in this sub-netted network and is considered a physical network in an
autonomous network. So it owns a network IP address which may looks like
168.1.2.0.
With the subnet mask, a bigger network can be cut into small pieces of
network. If we want to have more than two independent networks in a worknet, a
partition to the network must be performed. In this case, subnet mask must be
applied.
Page 32
24
For different network applications, the subnet mask may look like
255.255.255.240. This means it is a small network accommodating a maximum of
15 nodes in the network.
Default gateway:
For the routed packet, if the destination is not in the routing table, all the
traffic is put into the device with the designated IP address, known as default router.
Basically, it is a routing policy. The gateway setting is used for Trap Events Host
only in the switch.
For assigning an IP address to the switch, you just have to check what the IP
address of the network will be connected with the switch. Use the same network
address and append your host address to it.
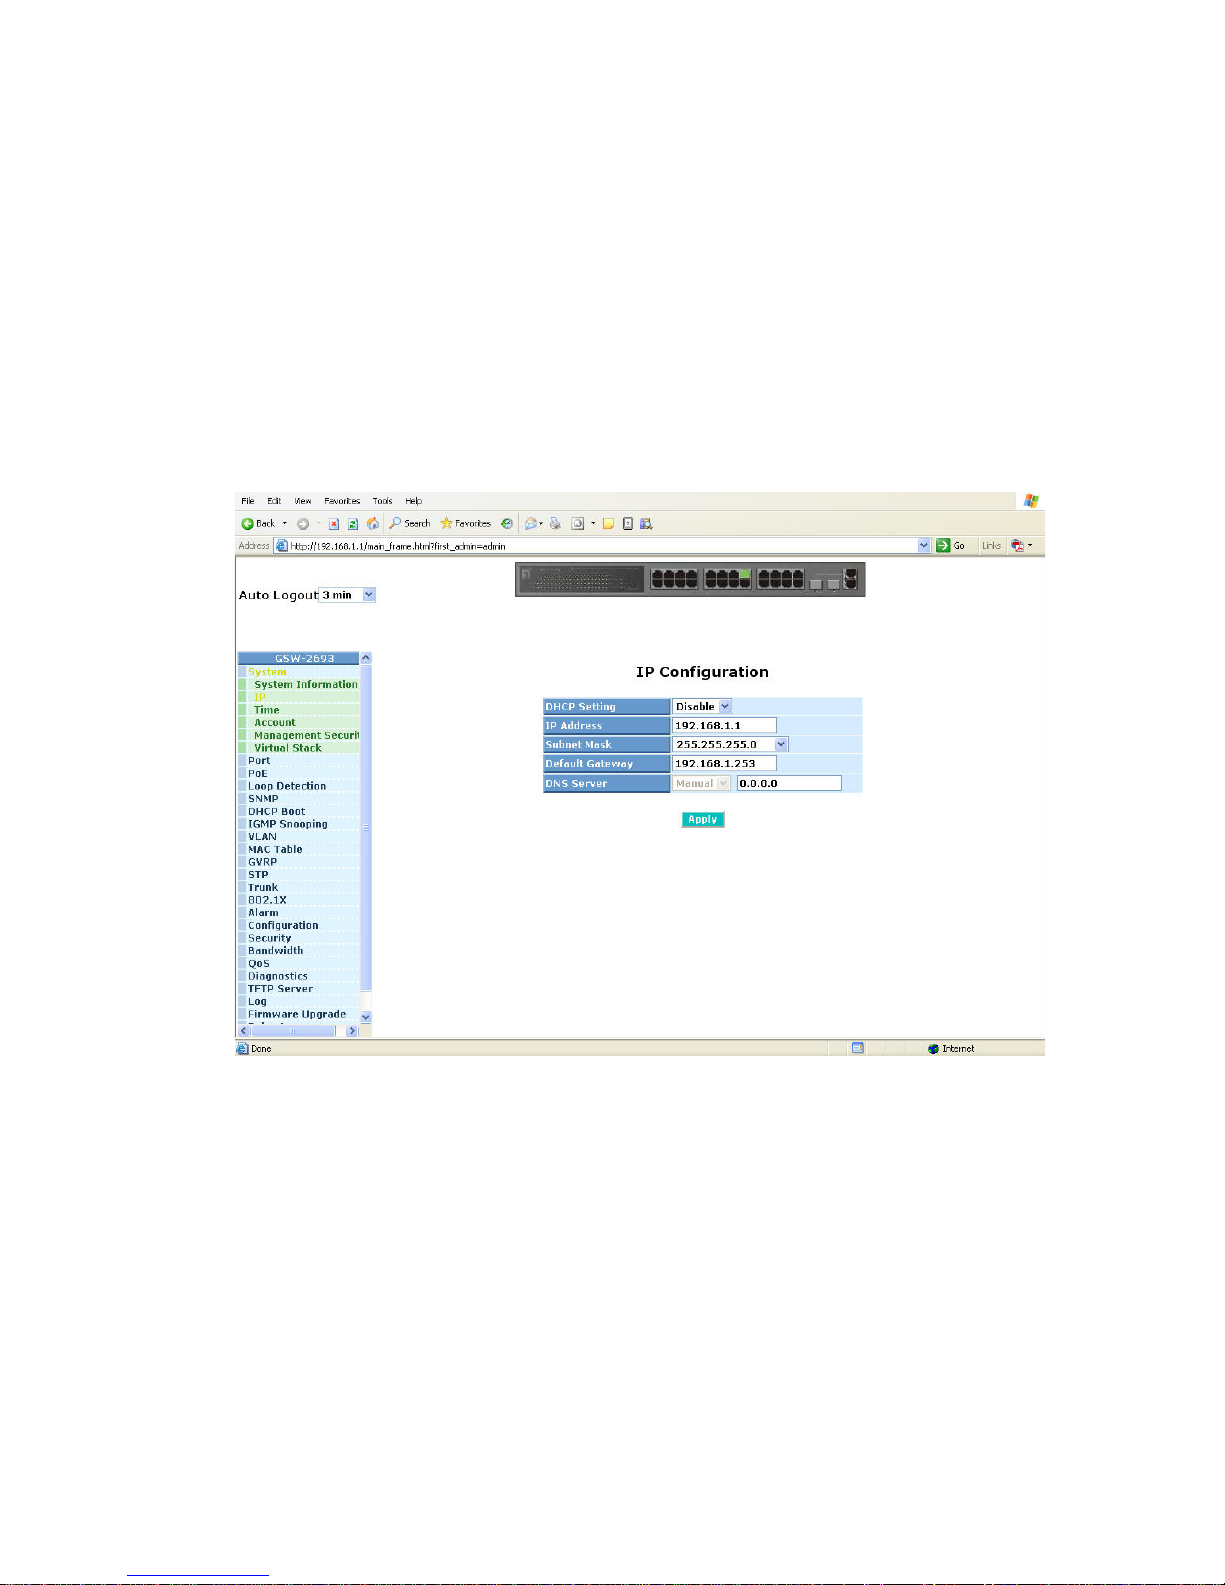
Fig. 2-12
First, IP Address: as shown in the Fig. 2-12, enter “192.168.1.1”, for instance.
For sure, an IP address such as 192.168.1.x must be set on your PC.
Second, Subnet Mask: as shown in the Fig. 2-12, enter “255.255.255.0”. Any
subnet mask such as 255.255.255.x is allowable in this case.
DNS:
The Domain Name Server translates human readable machine name to IP
address. Every machine on the Internet has a unique IP address. A server generally
has a static IP address. To connect to a server, the client needs to know the IP of
the server. However, user generally uses the name to connect to the server. Thus,
the switch DNS client program (such as a browser) will ask the DNS to resolve the
IP address of the named server.
Page 33
25
2-2. Typical Applications
The GSW-2693 implements 24 Fast Ethernet TP ports with auto MDIX and 2
Gigabit dual media ports with SFP for removable module supported comprehensive
fiber types of connection, including LC, BiDi LC for SFP. For more details on the
specification of the switch, please refer to Appendix A.
The switch is suitable for the following applications.
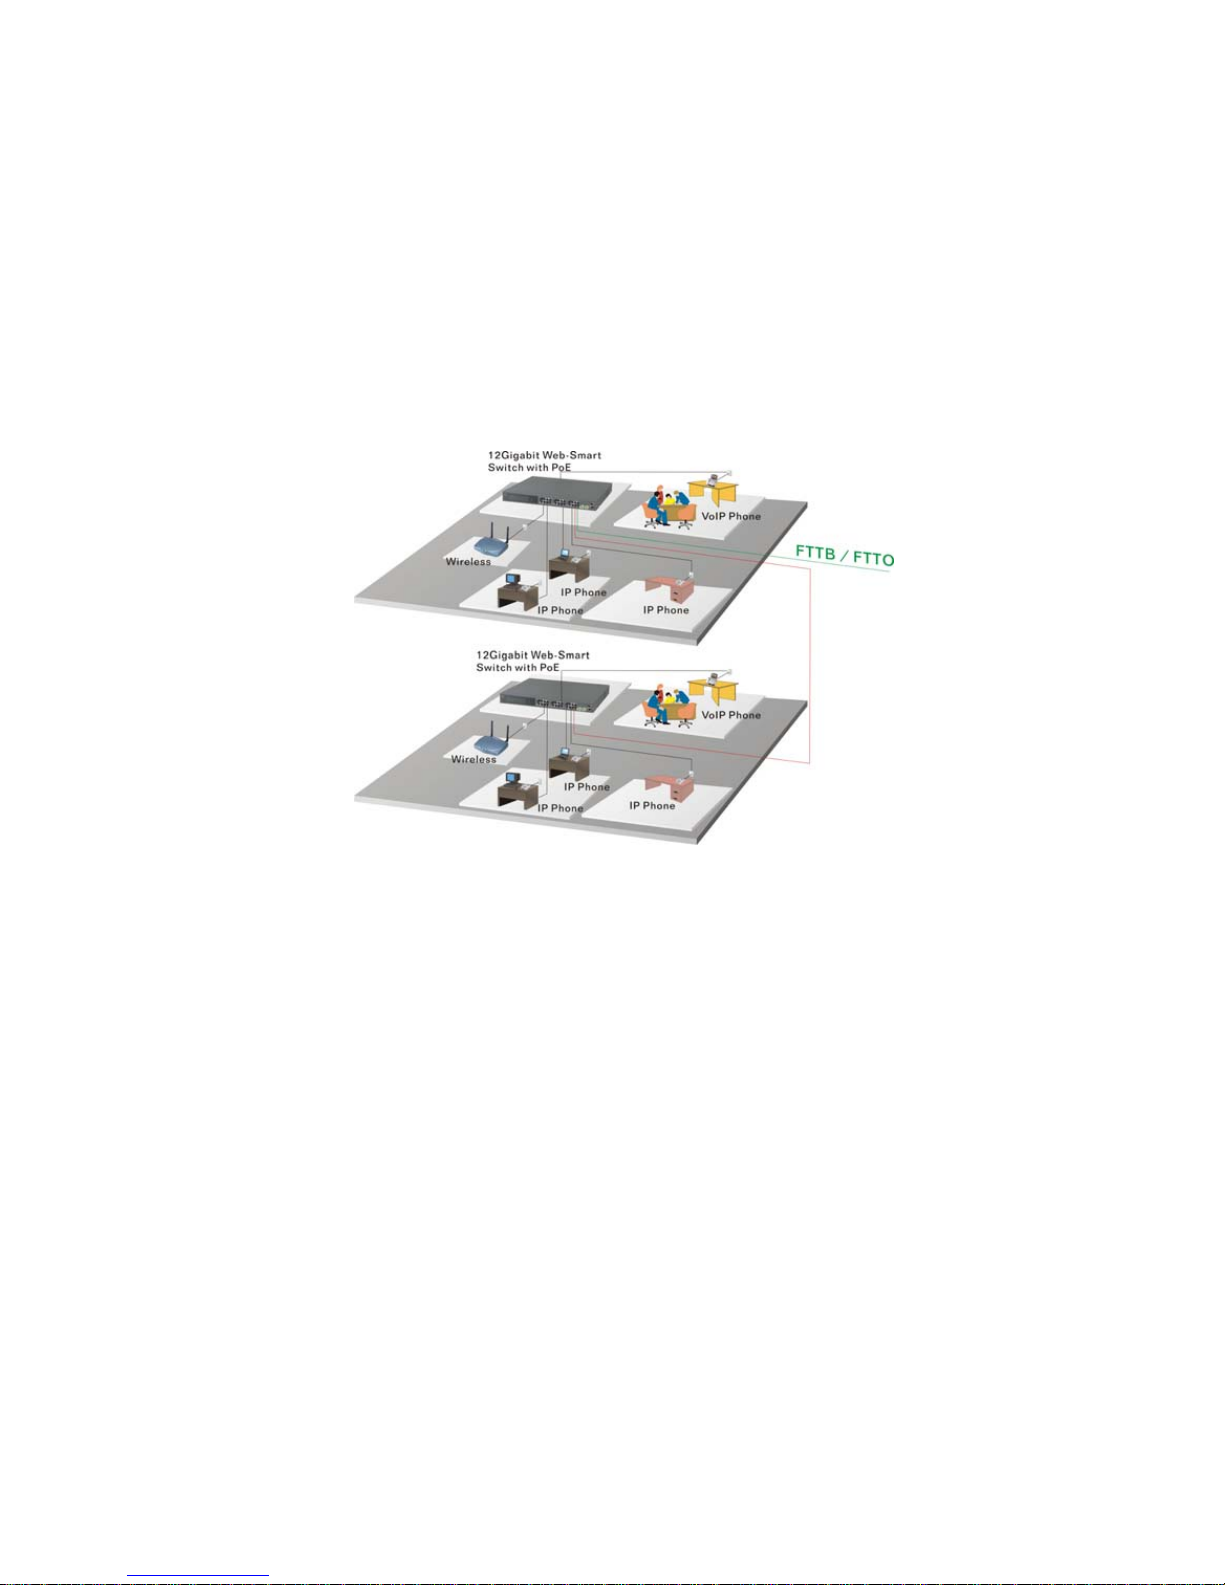
⎯ FTTB/FTTO application is used in carrier or ISP (See Fig. 2-13)
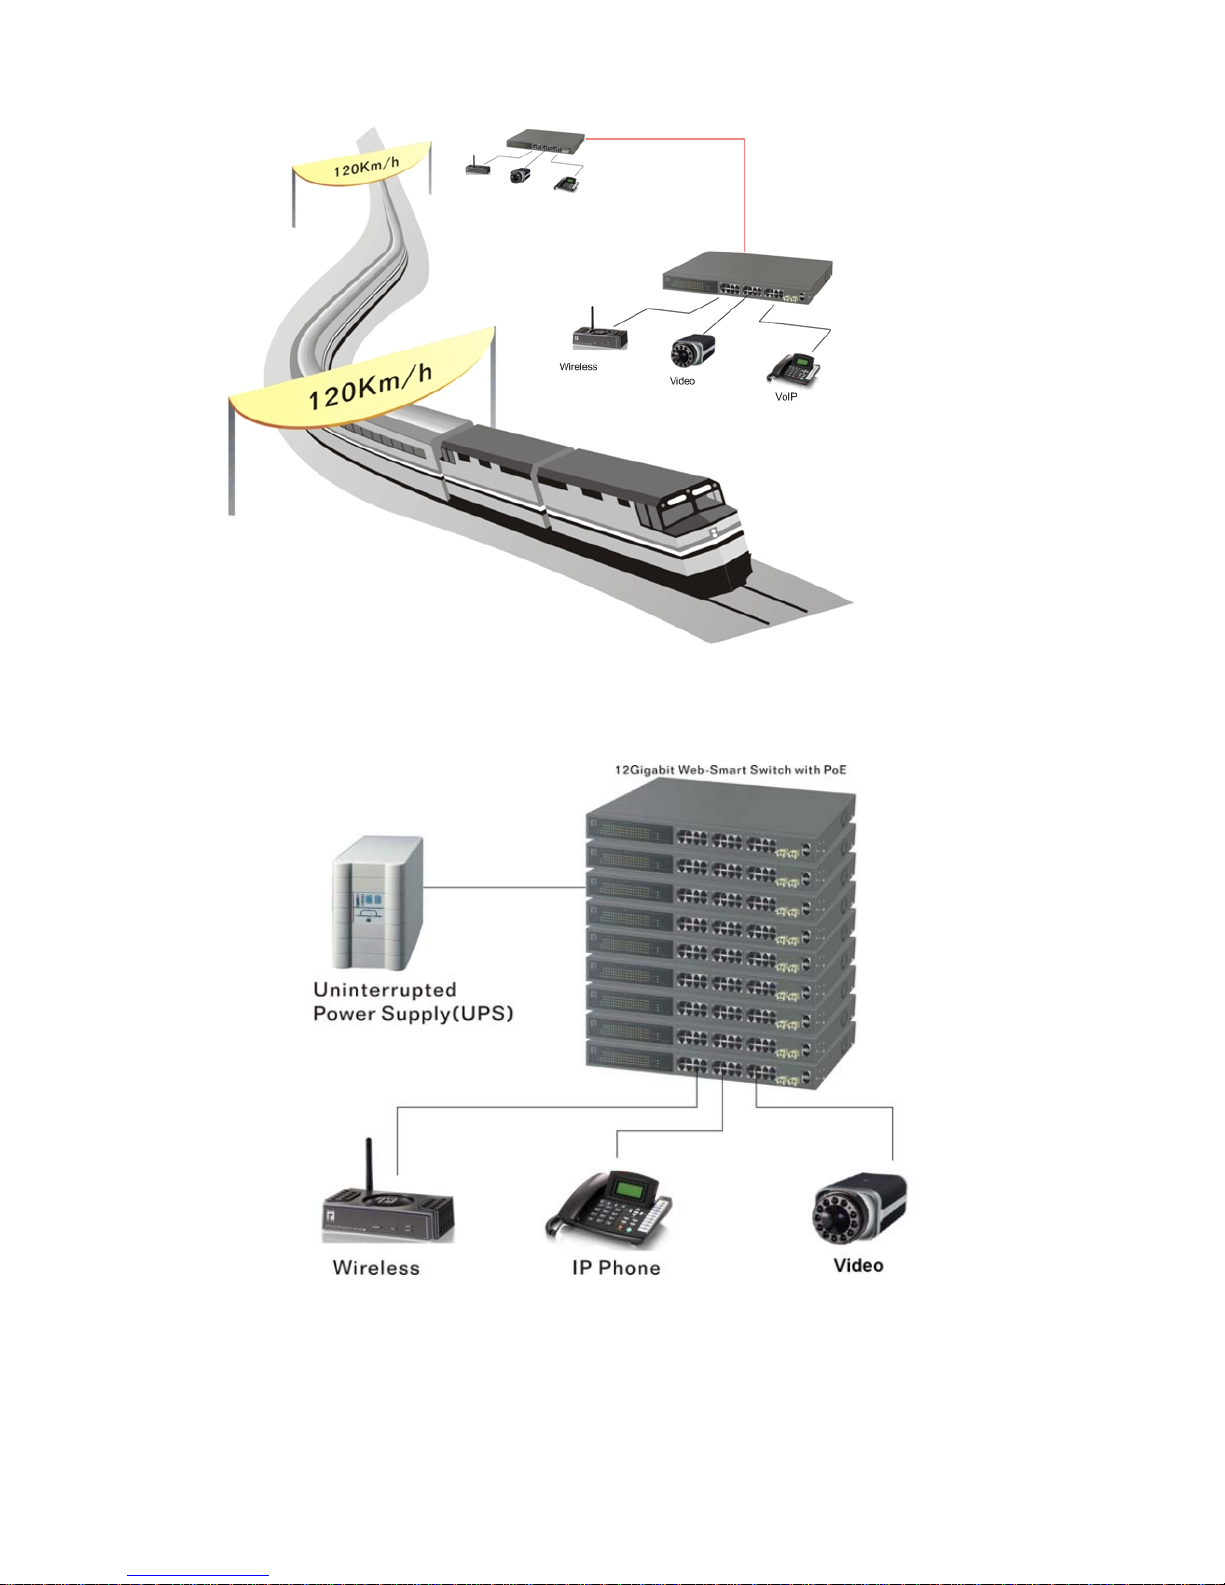
⎯ FTTH application is used in carrier or ISP (See Fig. 2-14)
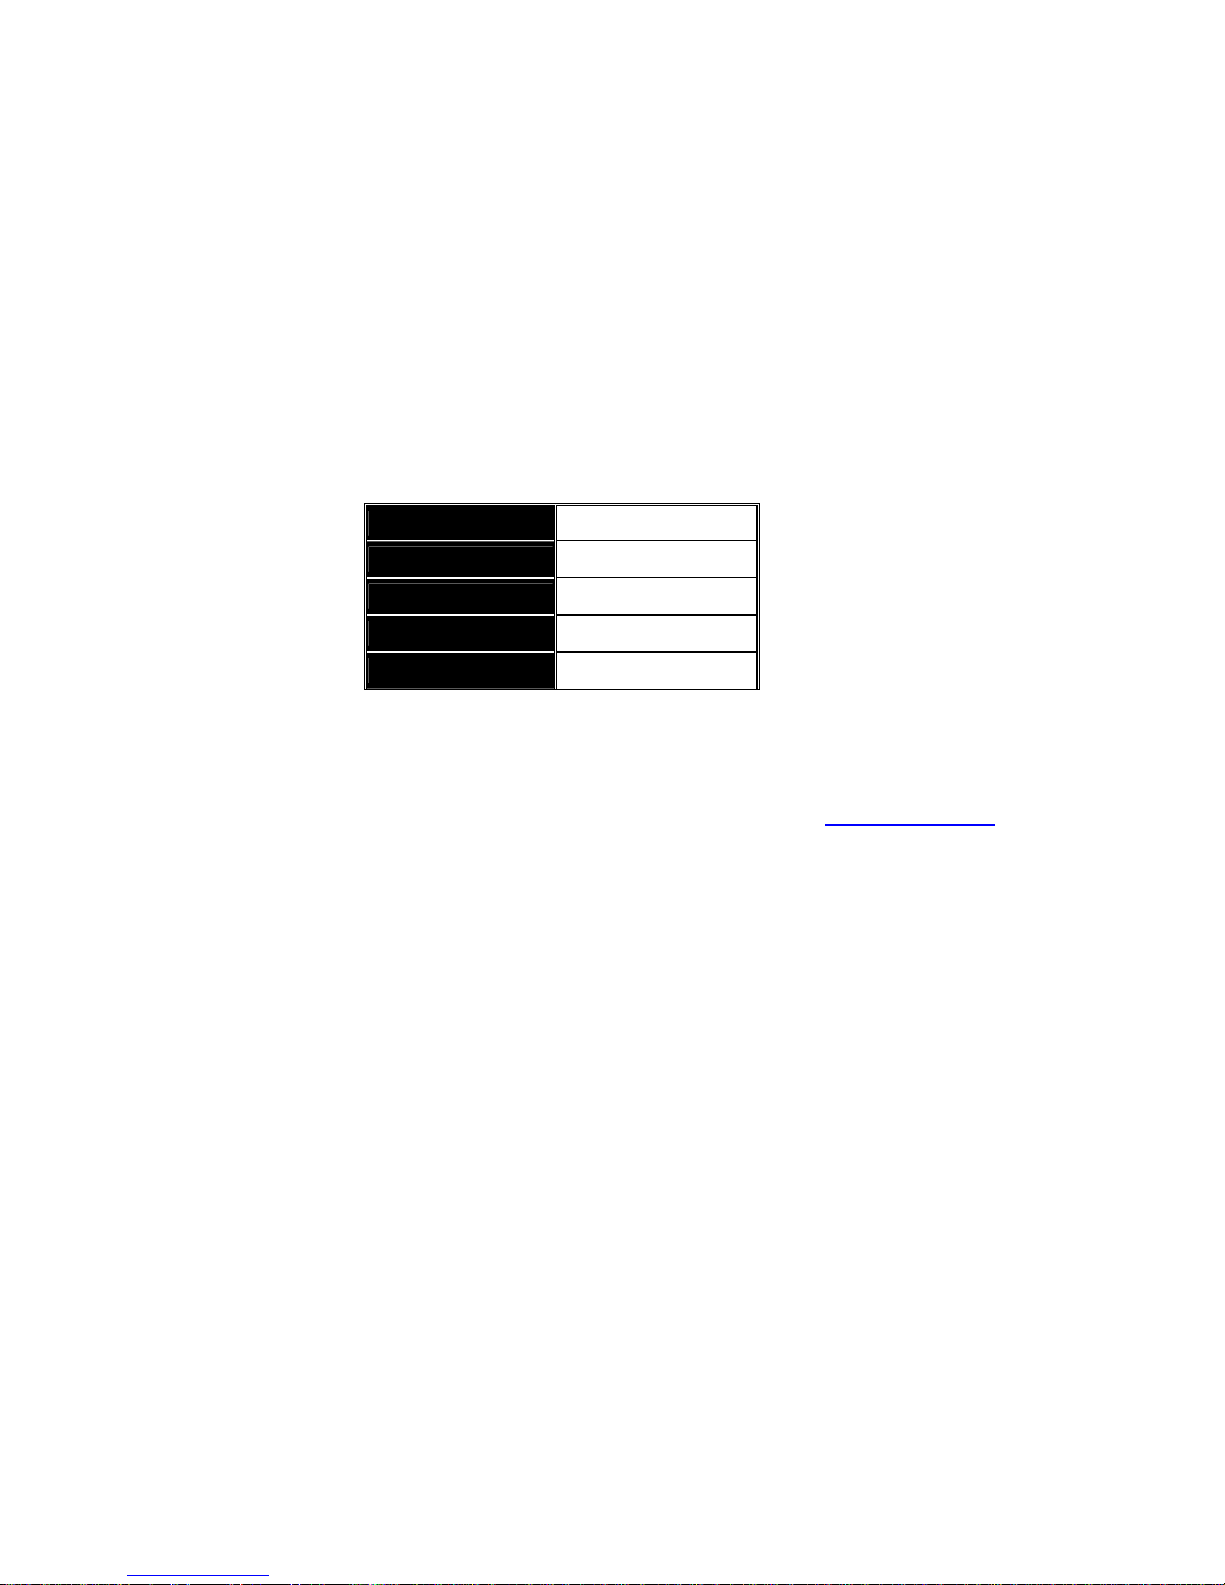
⎯ Daisy-Chain Fiber Network Connection (See Fig. 2-15)
Fig. 2-13 Network Connection of FTTB/FTTO
Fig. 2-13 is a system wide basic reference connection diagram. This diagram
demonstrates how the switch connects with other network devices and hosts.
Page 34
26
Fig. 2-14 Daisy-Chain Fiber Network Connection
Fig. 2-15 Uninterrupted Power Supply for IP Phone Application
Page 35
27
3. Operation of
Web-based Management
This chapter instructs you how to configure and manage the GSW-2693
through the web user interface it supports, to access and manage the 24
10/100Mbps TP + 2 Gigabit dual media ports with TP/SFP Fiber management
Ethernet switch. With this facility, you can easily access and monitor through any
one port of the switch all the status of the switch, including MIBs status, each port
activity, Spanning tree status, port aggregation status, multicast traffic, VLAN and
priority status, even illegal access record and so on.
The default values of the managed switch are listed in the table below:
IP Address
192.168.1.1
Subnet Mask
255.255.255.0
Default Gateway
192.168.1.254
Username
admin
Password
admin
Table 3-1
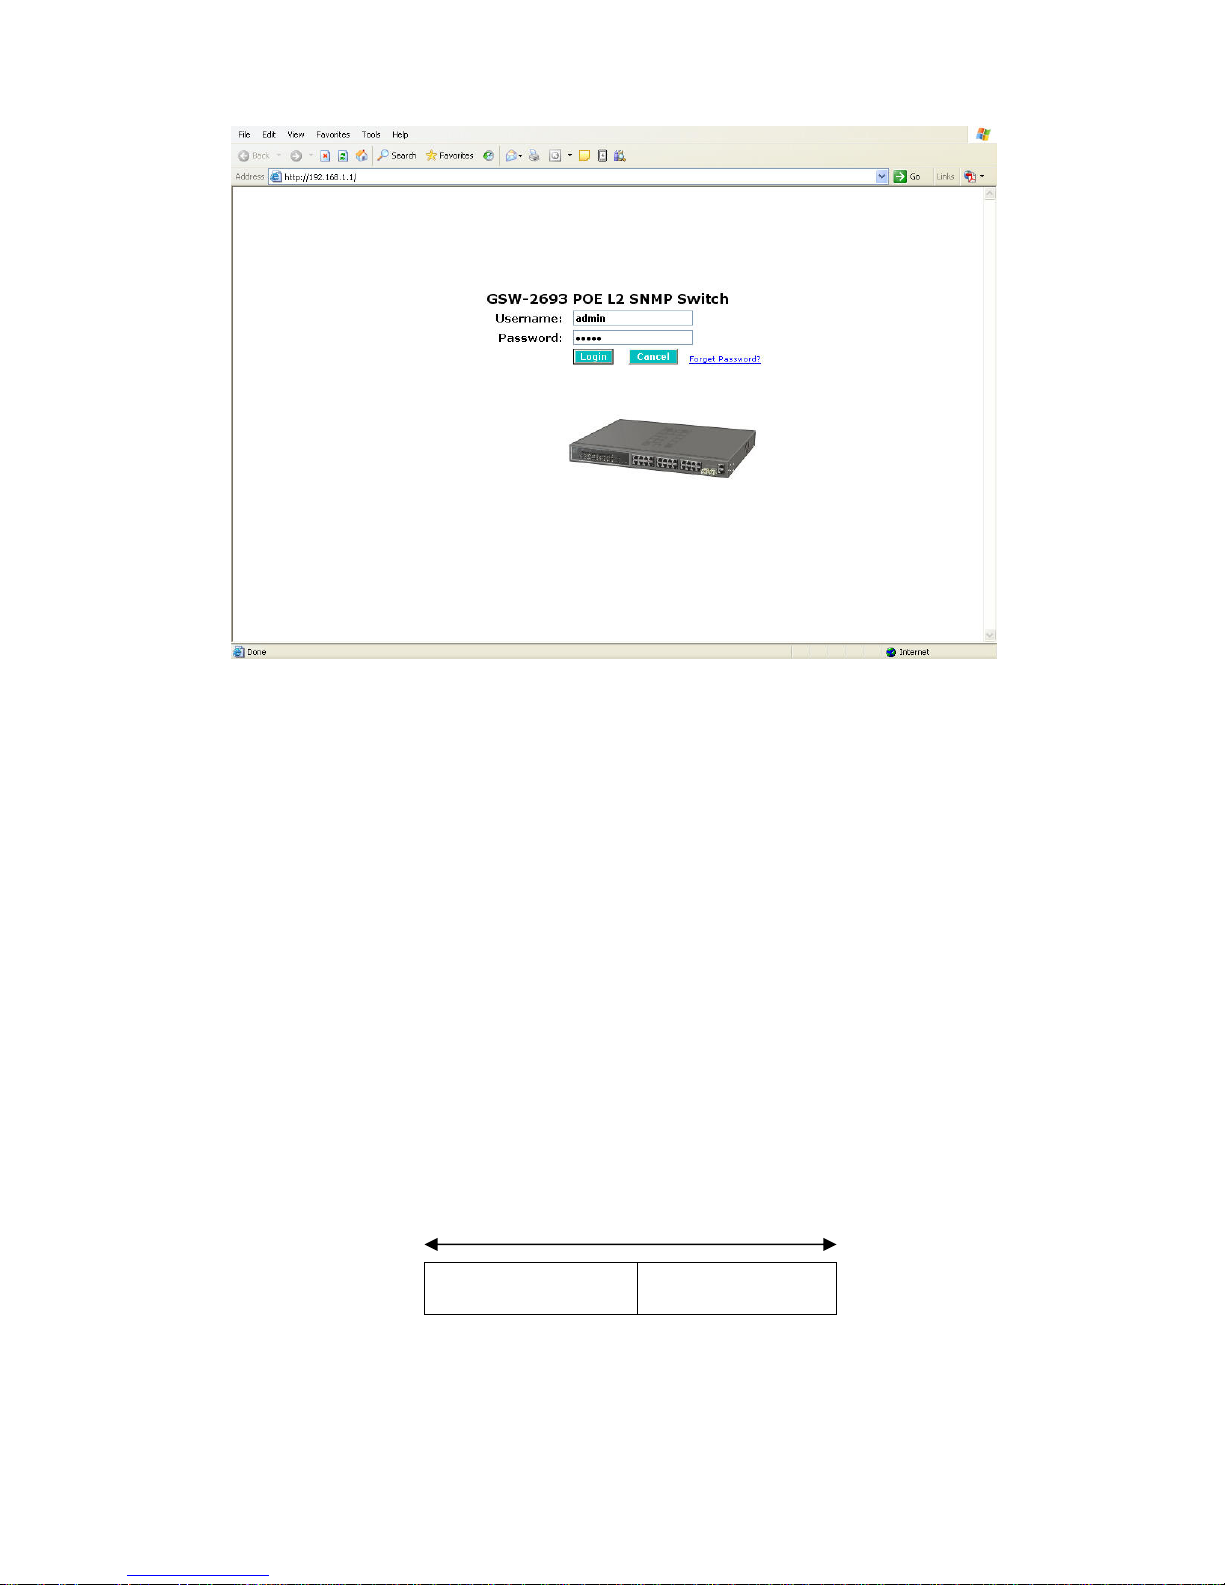
After the managed switch has been finished configuration in the CLI via the
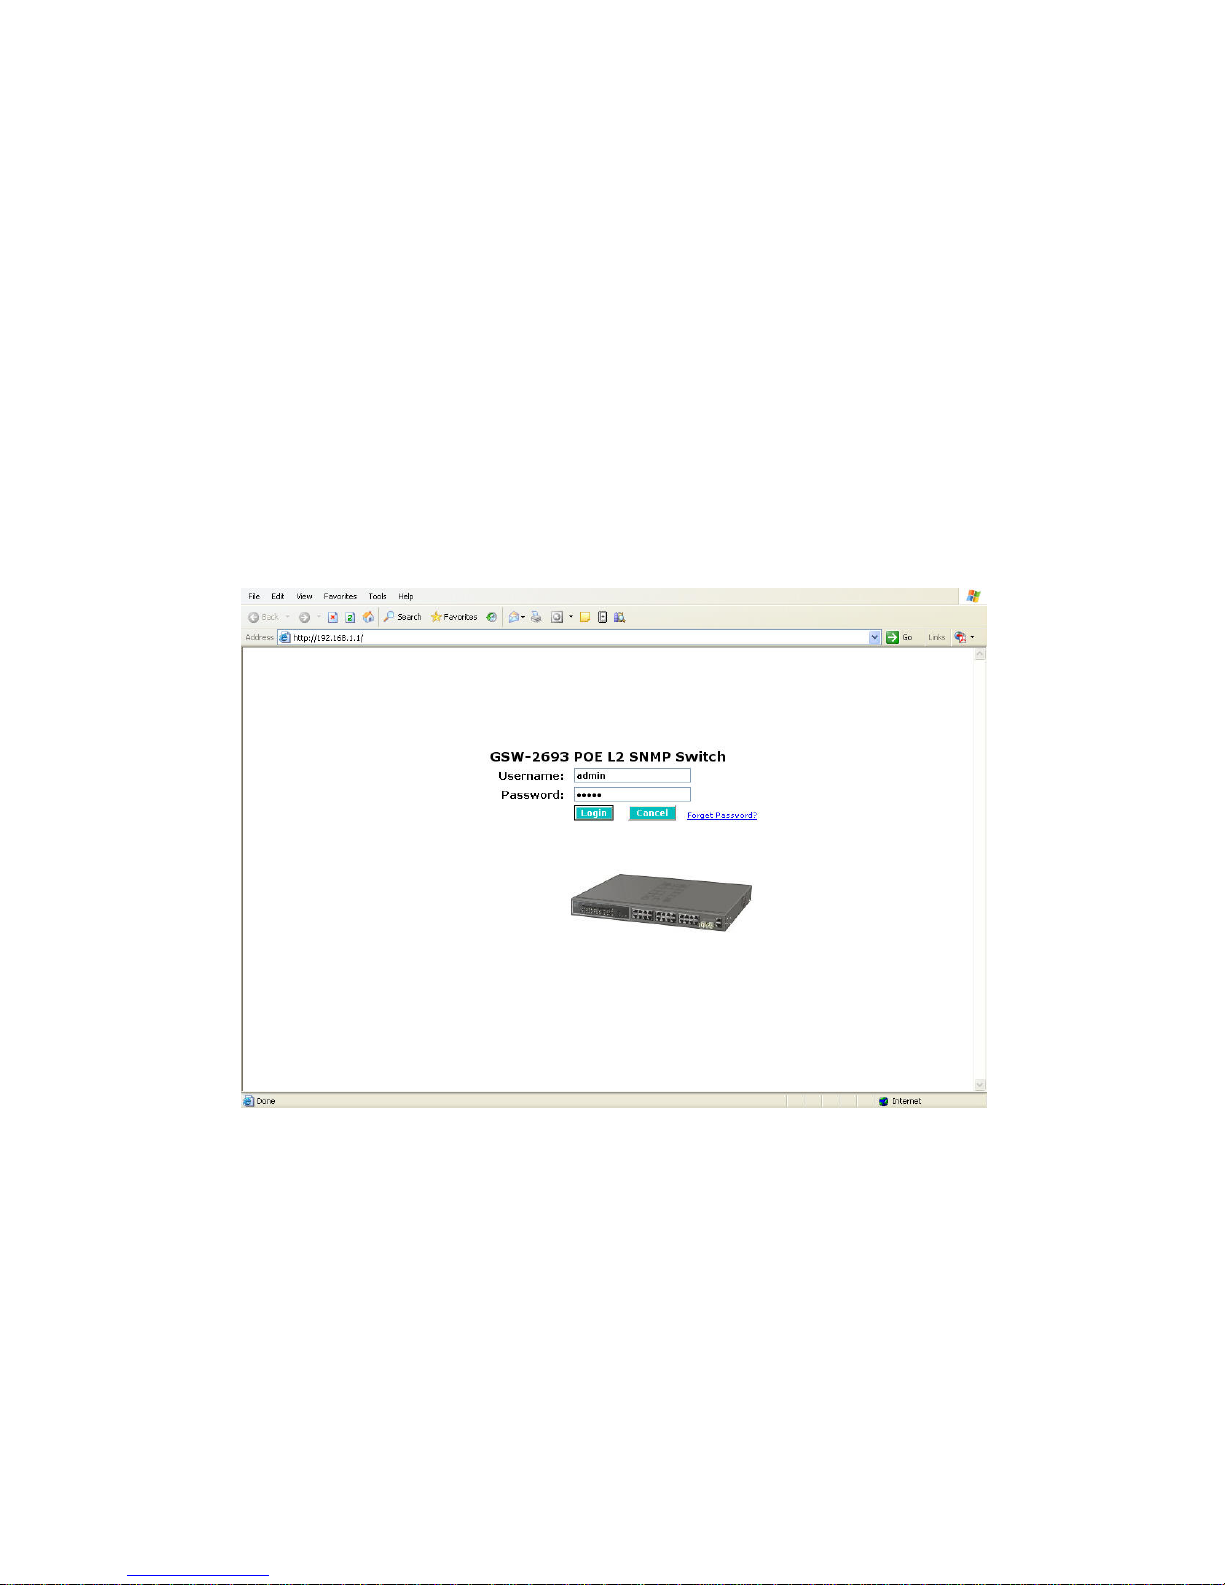
switch’s serial interface, you can browse it. For instance, type
http://192.168.1.1 in
the address row in a browser, it will show the following screen (see Fig.3-1) and ask
you inputting username and password in order to login and access authentication.
The default username and password are both “admin”. For the first time to use,
please enter the default username and password, then click the <Login> button.
The login process now is completed.
Just click the link of “Forget Password” in WebUI (See Fig. 3-1) or input
“Ctrl+Z” in CLI’s login screen (See Fig. 4-1~4-2) in case the user forgets the
manager’s password. Then, the system will display a serial No. for the user. Write
down this serial No. and contact your vendor, the vendor will give you a temporary
password. Use this new password as ID and Password, and it will allow the user to
login the system with manager authority temporarily. Due to the limit of this new
password, the user only can login the system one time, therefore, please modify
your password immediately after you login in the system successfully.
In this login menu, you have to input the complete username and password
respectively, the switch will not give you a shortcut to username automatically. This
looks inconvenient, but safer.
Page 36
28
In the switch, it supports a simple user management function allowing only
one administrator to configure the system at the same time. If there are two or more
users using administrator’s identity, the switch will allow the only one who logins first
to configure the system. The rest of users, even with administrator’s identity, can
only monitor the system. For those who have no administrator’s identity, can only
monitor the system. There are only a maximum of three users able to login
simultaneously in the switch.
To optimize the display effect, we recommend you use Microsoft IE 6.0
above, Netscape V7.1 above or FireFox V1.00 above and have the resolution
1024x768. The switch supported neutral web browser interface.
In Fig. 3-2, for example, left section is the whole function tree with web user
interface and we will travel it through this chapter.
Fig. 3-1
Page 37
29
3-1. Overview
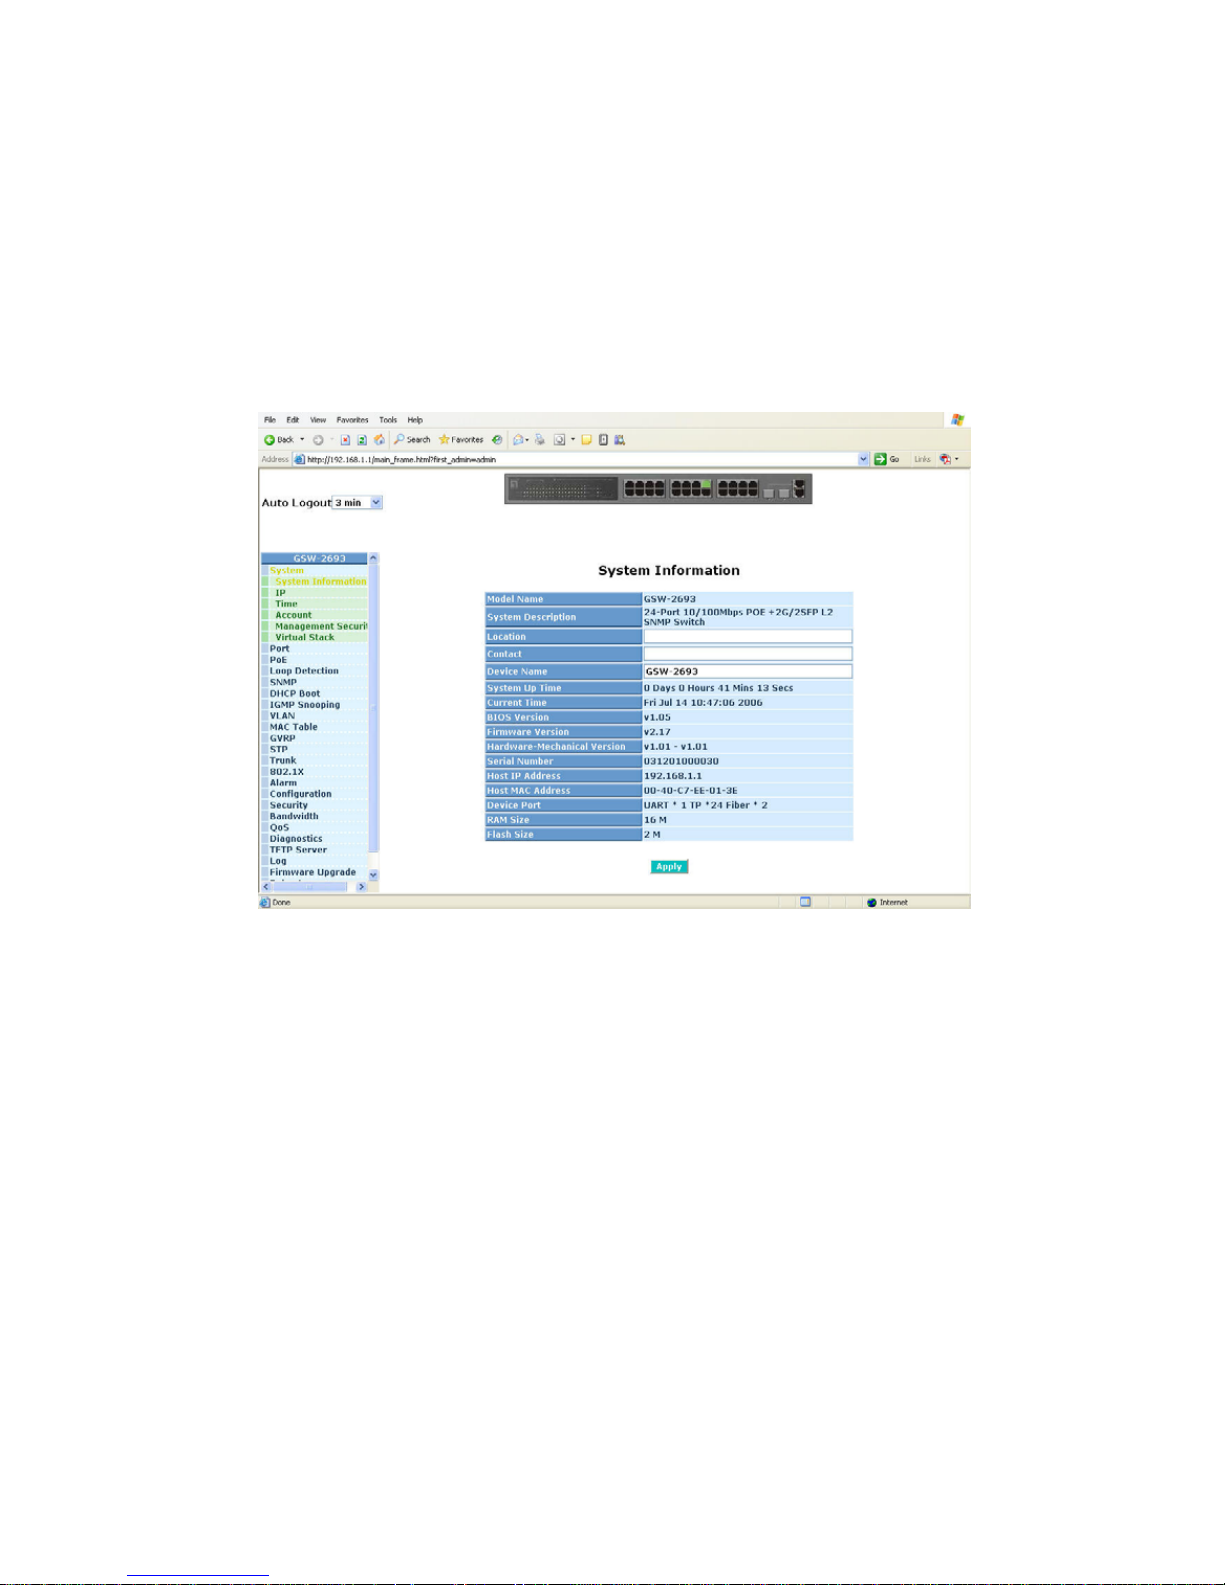
After you login, the switch shows you the system information as Fig. 3-2. This
page is default and tells you the basic information of the system, including “Model
Name”, “System Description”, “Location”, “Contact”, “Device Name”, “System Up
Time”, “Current Time”, “BIOS Version”, “Firmware Version”, “Hardware-Mechanical
Version”, “Serial Number”, “Host IP Address”, “Host MAC Address”, “Device Port”,
“RAM Size” and “Flash Size”. With this information, you will know the software
version used, MAC address, serial number, how many ports good and so on. This is
helpful while malfunctioning.
Fig. 3-2
•
The Information of Page Layout
⎯ On the top side, it shows the front panel of the switch. In the front panel, the
linked ports will display green; as to the ports, which are link off, they will be
dark. For the optional modules, the slot will show only a cover plate if no
module exists and will show a module if a module is present. The image of
module depends on the one you inserted. The same, if disconnected, the port
will show just dark, if linked, green.
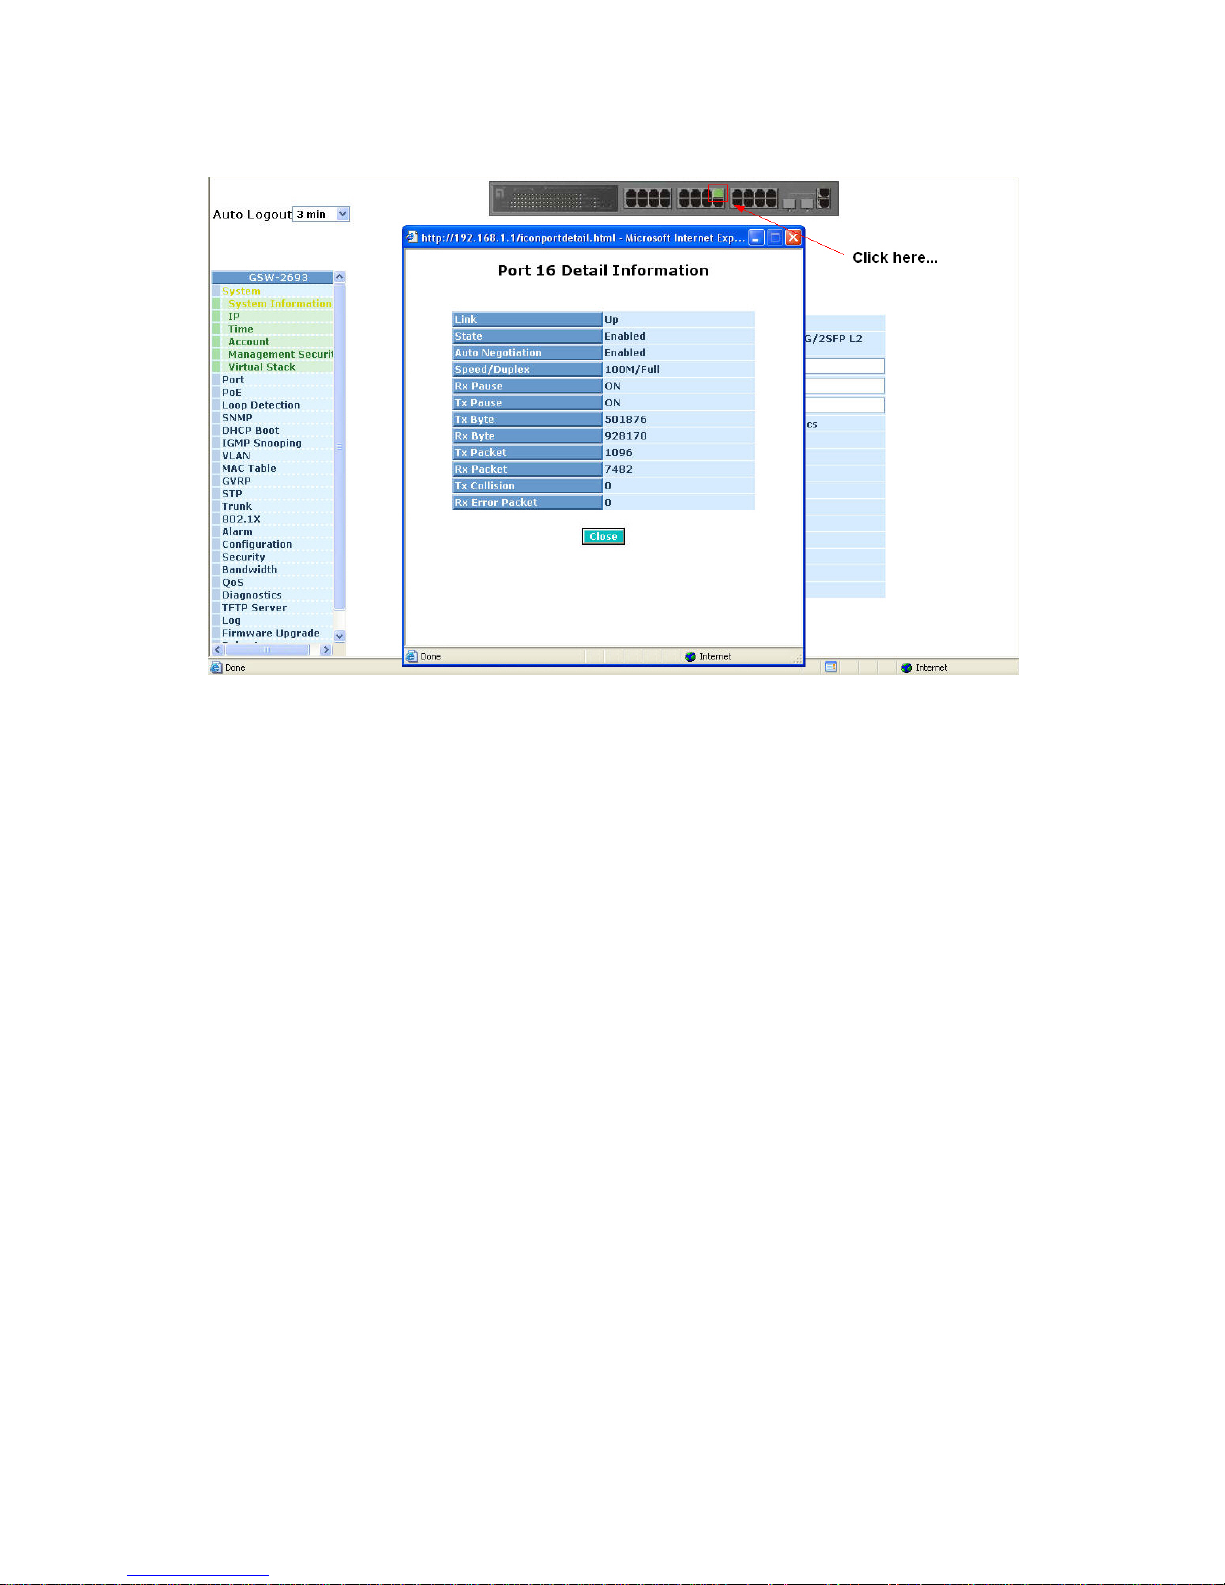
In this device, there are clicking functions on the panel provided for the
information of the ports. These are very convenient functions for browsing the
information of a single port. When clicking the port on the front panel, an
information window for the port will be pop out. (See Fig. 3-3)
Page 38
30
Fig. 3-3 port detail information
In Fig. 3-3, it shows the basic information of the clicked port. With this, you’ll
see the information about the port status, traffic status and bandwidth rating for
egress and ingress respectively.
⎯ On the left-top corner, there is a pull-down list for Auto Logout. For the sake of
security, we provide auto-logout function to protect you from illegal user as you
are leaving. If you do not choose any selection in Auto Logout list, it means
you turn on the Auto Logout function and the system will be logged out
automatically when no action on the device 3 minutes later. If OFF is chosen,
the screen will keep as it is. Default is ON.
⎯ On the left side, the main menu tree for web is listed in the page. They are
hierarchical menu. Open the function folder, a sub-menu will be shown. The
functions of each folder are described in its corresponded section respectively.
When clicking it, the function is performed. The following list is the full function
tree for web user interface.
Page 39
31
Port
Loop Detection
DHCP Boot
System
PoE
SNMP
IGMP Snoopin
g
VLAN
Root
MAC Table
GVRP
STP
Trunk
802.1x
A
larm
Configuration
Securit
y
Bandwidth
QoS
Diagnostics
TFTP Server
Log
Firmware Upgrade
Reboot
Logout
Page 40
32
3-1-1. System Information
Function name:
System Information
Function description:
Show the basic system information.
Parameter description:
Model name:
The model name of this device.
System description:
As it is, this tells what this device is. Here, it is “24-Port 10/100BaseT/TX
Managed PoE Switch”.
Location:
Basically, it is the location where this switch is put. User-defined.
Contact:
For easily managing and maintaining device, you may write down the
contact person and phone here for getting help soon. You can configure
this parameter through the device’ s user interface or SNMP.
Device name:
The name of the switch. User-defined. Default is GSW-2693.
System up time:
The time accumulated since this switch is powered up. Its format is day,
hour, minute, second.
Current time:
Show the system time of the switch. Its format: day of week, month, day,
hours : minutes : seconds, year. For instance, Tue Apr 20 23:25:58 2005
BIOS version:
The version of the BIOS in this switch.
Firmware version:
The firmware version in this switch.
Hardware-Mechanical version:
The version of Hardware and Mechanical. The figure before the hyphen
is the version of electronic hardware; the one after the hyphen is the
version of mechanical.
Serial number:
The number is assigned by the manufacturer.
Page 41
33
Host IP address:
The IP address of the switch.
Host MAC address:
It is the Ethernet MAC address of the management agent in this switch.
Device Port:
Show all types and numbers of the port in the switch.
RAM size:
The size of the DRAM in this switch.
Flash size:
The size of the flash memory in this switch.
Page 42
34
3-1-2. IP Configuration
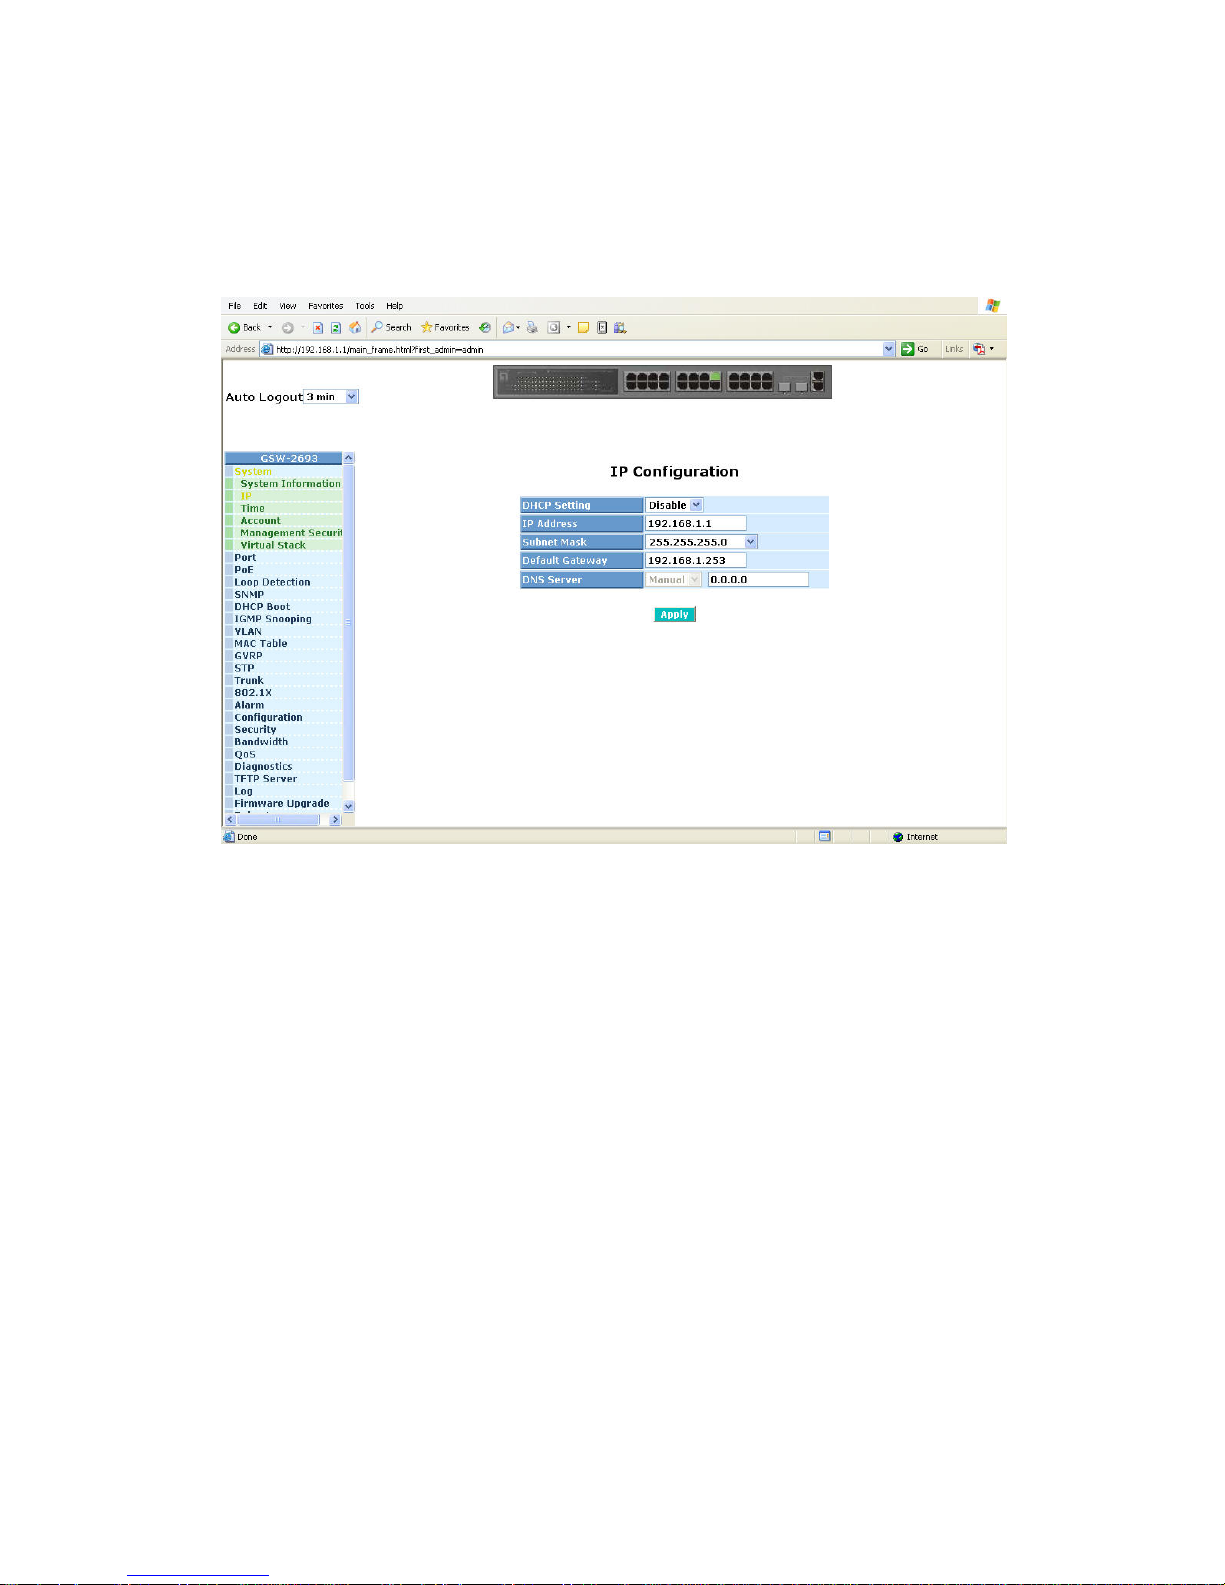
IP configuration is one of the most important configurations in the switch. Without the
proper setting, network manager will not be able to manage or vie w the device. The switch
supports both manual IP address setting and automatic IP address setting via DHCP server.
When IP address is changed, you must reboot the switch to have the setting taken effect and
use the new IP to browse for web management and CLI management.
Fig. 3-4 IP Address Configuration
Function name:
IP Configuration
Function description:
Set IP address, subnet mask, default gateway and DNS for the switch.
Parameter description:
DHCP Setting:
DHCP is the abbreviation of Dynamic Host Configuration Protocol. Here
DHCP means a switch to turn ON or OFF the function.
The switch supports DHCP client used to get an IP address automatically
if you set this function “Enable”. When enabled, the switch will issue the
request to the DHCP server resided in the network to get an IP address.
If DHCP server is down or does not exist, the switch will issue the
request and show IP address is under requesting, until the DHCP server
is up. Before getting an IP address from DHCP server, the device will not
continue booting procedures. If set this field “Disable”, you’ll have to
input IP address manually. For more details about IP address and DHCP,
please see the Section 2-1-5 “IP Address Assignment” in this manual.
Default: Disable
Page 43
35
IP address:
Users can configure the IP settings and fill in new values if users set the
DHCP function “Disable”. Then, cli ck <Apply> button to update.
When DHCP is disabled, Default: 192.168.1.1
If DHCP is enabled, this field is filled by DHCP server and will not allow
user manually set it any more.
Subnet mask:
Subnet mask is made for the purpose to get more network address
because any IP device in a network must own its IP address, composed
of Network address and Host address, otherwise can’t communicate with
other devices each other. But unfortunately, the network classes A, B,
and C are all too large to fit for almost all networks, hence, subnet mask
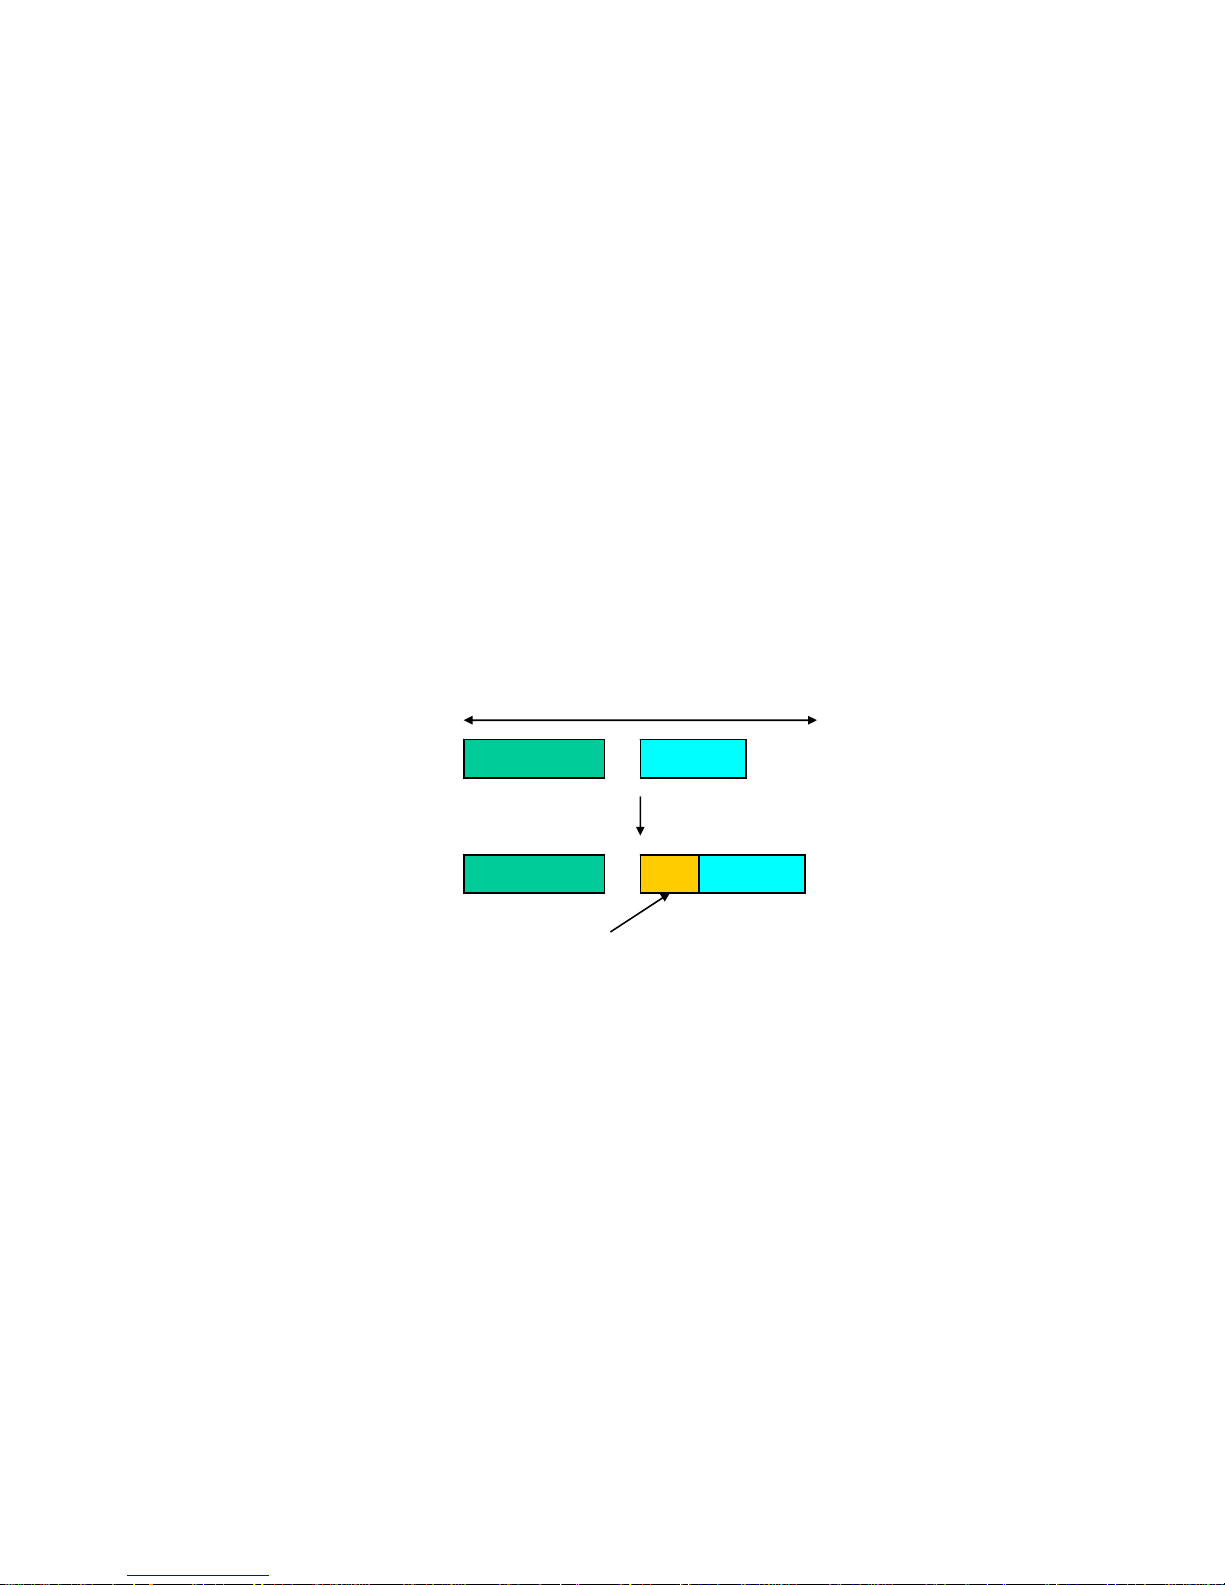
is introduced to solve this problem. Subnet mask uses some bits from
host address and makes an IP address looked Network address, Subnet
mask number and host address. It is shown in the following figure. This
reduces the total IP number of a network able to support, by the amount
of 2 power of the bit number of subnet number (2^(bit number of subnet
number)).
Subnet mask is used to set the subnet mask value, which should be the
same value as that of the other devices resided in the same network it
attaches.
For more information, please also see the Section 2-1-5 “IP Address
Assignment” in this manual.
Default: 255.255.255.0
Default gateway:
Set an IP address for a gateway to handle those packets that do not
meet the routing rules predefined in the device. If a packet does not meet
the criteria for other pre-defined path, it must be forwarded to a default
router on a default path. This means any packet with undefined IP
address in the routing table will be sent to this device unconditionally.
Default: 192.168.1.254
32 bits
Network ID Host ID
Network ID Host ID
Subnet number
Page 44
36
DNS:
It is Domain Name Server used to serve the translation between IP
address and name address.
The switch supports DNS client function to re-route the mnemonic name
address to DNS server to get its associated IP address for accessing
Internet. User can specify a DNS IP address for the switch. With this, the
switch can translate a mnemonic name address into an IP address.
There are two ways to specify the IP address of DNS. One is fixed mode,
which manually specifies its IP address, the other is dynamic mode,
which is assigned by DHCP server while DHCP is enabled. DNS can
help you easily remember the mnemonic address name with the
meaningful words in it. Default is no assignment of DNS address.
Default: 0.0.0.0
Page 45
37
3-1-3. Time Configuration
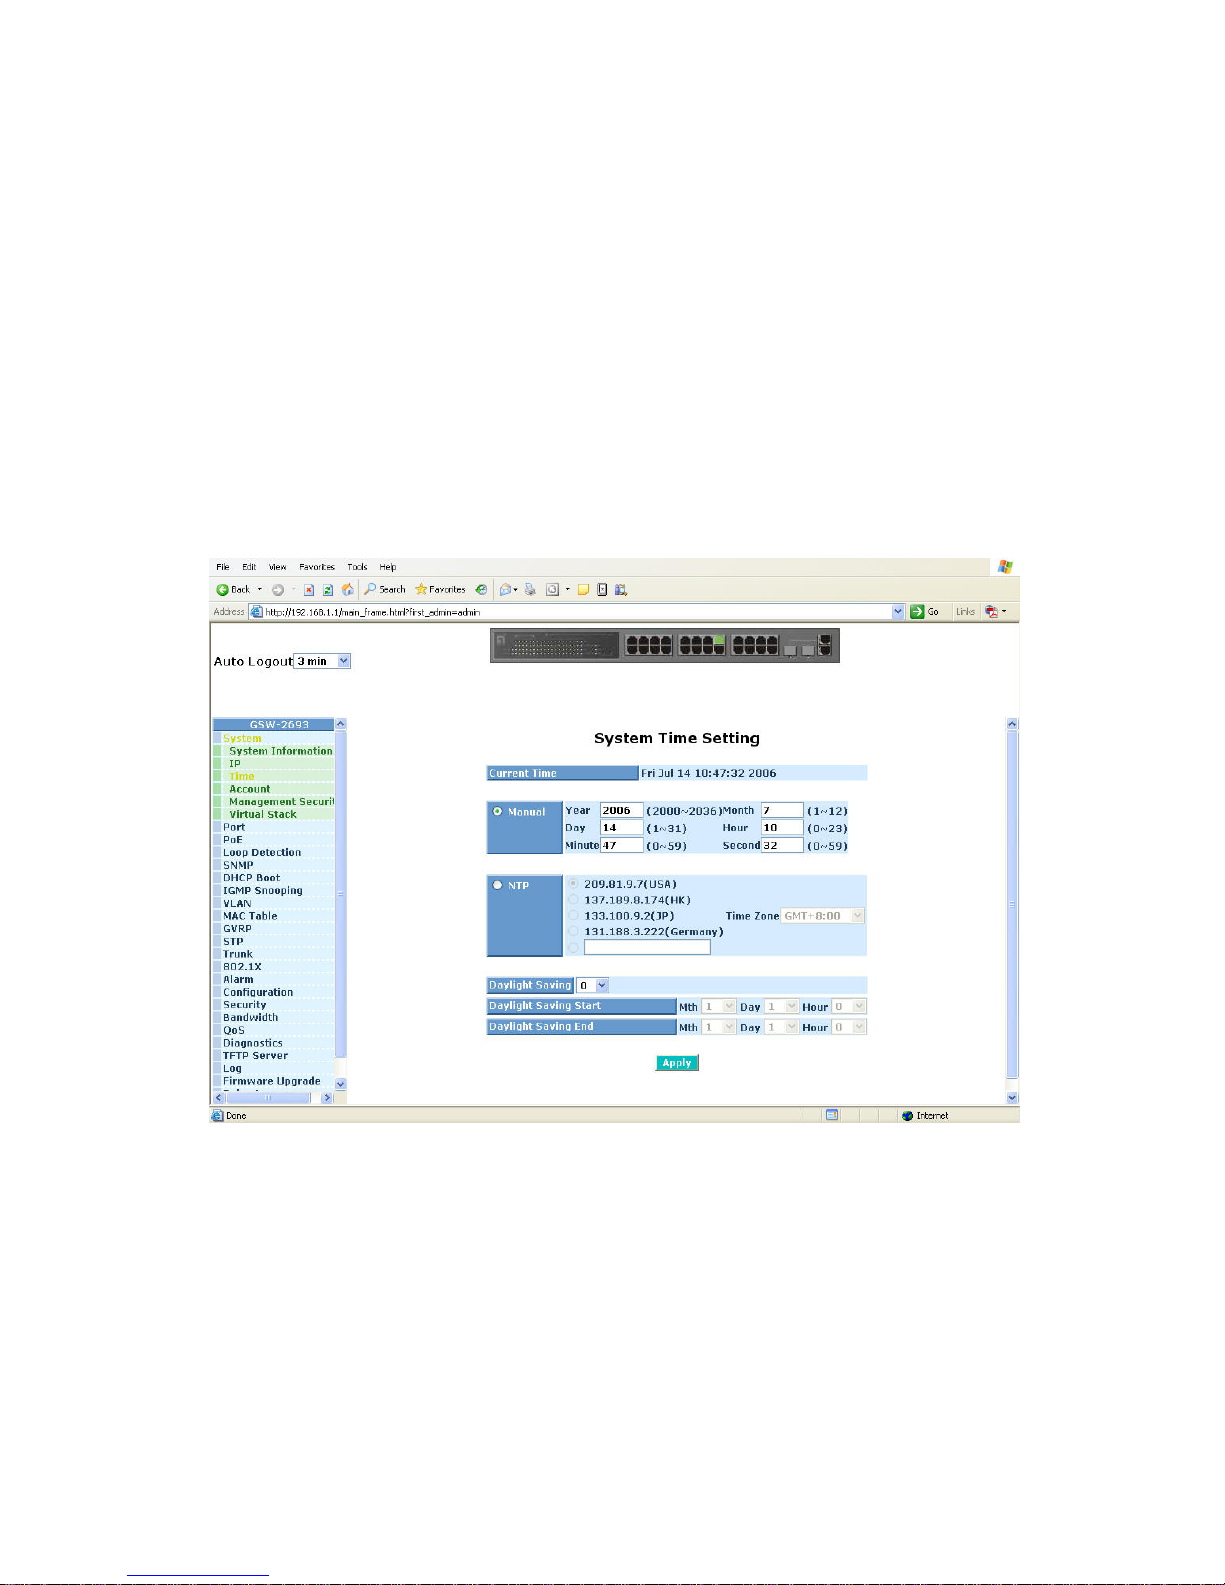
The switch provides manual and automatic ways to set the system time via
NTP. Manual setting is simple and you just input “Year”, “Month”, “Day”, “Hour”,
“Minute” and “Second” within the valid value range indicated in each item. If you
input an invalid value, for example, 61 in minute, the switch will clamp the figure to
59.
NTP is a well-known protocol used to synchronize the clock of the switch
system time over a network. NTP, an internet draft standard formalized in
RFC 1305,
has been adopted on the system is version 3 protocol. The switch provides four
built-in NTP server IP addresses resided in the Internet and an user-defined NTP
server IP address. The time zone is Greenwich-centered which uses the expression
form of GMT+/- xx hours.
Function name:
Time
Function description:
Set the system time by manual input or set it by syncing from Time servers.
The function also supports daylight saving for different area’s time adjustment.
Parameter description:
Current Time:
Show the current time of the system.
Manual:
This is the function to adjust the time manually. Filling the valid figures in
the fields of Year, Month, Day, Hour, Minute and Second respectively and
press <Apply> button, time is adjusted. The valid figures for the
parameter Year, Month, Day, Hour, Minute and Second are >=2000, 1-12,
1-31, 0-23, 0-59 and 0-59 respectively. Input the wrong figure and press
<Apply> button, the device will reject the time adjustment request. There
is no time zone setting in Manual mode.
Default: Year = 2000, Month = 1, Day = 1
Hour = 0, Minute = 0, Second = 0
Page 46
38
NTP:
NTP is Network Time Protocol and is used to sync the network time
based Greenwich Mean Time (GMT). If use the NTP mode and select a
built-in NTP time server or manually specify an user-defined NTP server
as well as Time Zone, the switch will sync the time in a short after
pressing <Apply> button. Though it synchronizes the time automatically,
NTP does not update the time periodically without user’s processing.
Time Zone is an offset time off GMT. You have to select the time zone
first and then perform time sync via NTP because the switch will combine
this time zone offset and updated NTP time to come out the local time,
otherwise, you will not able to get the correct time. The switch supports
configurable time zone from –12 to +13 step 1 hour.
Default Time zone: +8 Hrs.
Daylight Saving:
Daylight saving is adopted in some countries. If set, it will adjust the time
lag or in advance in unit of hours, according to the starting date and the
ending date. For example, if you set the day light saving to be 1 hour.
When the time passes over the starting time, the system time will be
increased one hour after one minute at the time since it passed over. And
when the time passes over the ending time, the system time will be
decreased one hour after one minute at the time since it passed over.
The switch supports valid configurable day light saving time is –5 ~ +5
step one hour. The zero for this parameter means it need not have to
adjust current time, equivalent to in-act daylight saving. You don’t have to
set the starting/ending date as well. If you set daylight saving to be nonzero, you have to set the starting/ending date as well; otherwise, the
daylight saving function will not be activated.
Default for Daylight Saving: 0.
The following parameters are configurable for the function Daylight
Saving and described in detail.
Day Light Saving Start :
This is used to set when to start performing the day light saving time.
Mth:
Range is 1 ~ 12.
Default: 1
Day:
Range is 1 ~ 31.
Default: 1
Hour:
Range is 0 ~ 23.
Default: 0
Page 47
39
Day Light Saving End :
This is used to set when to stop performing the daylight saving time.
Mth:
Range is 1 ~ 12.
Default: 1
Day:
Range is 1 ~ 31.
Default: 1
Hour:
Range is 0 ~ 23.
Default: 0
Fig. 3-5
Page 48
40
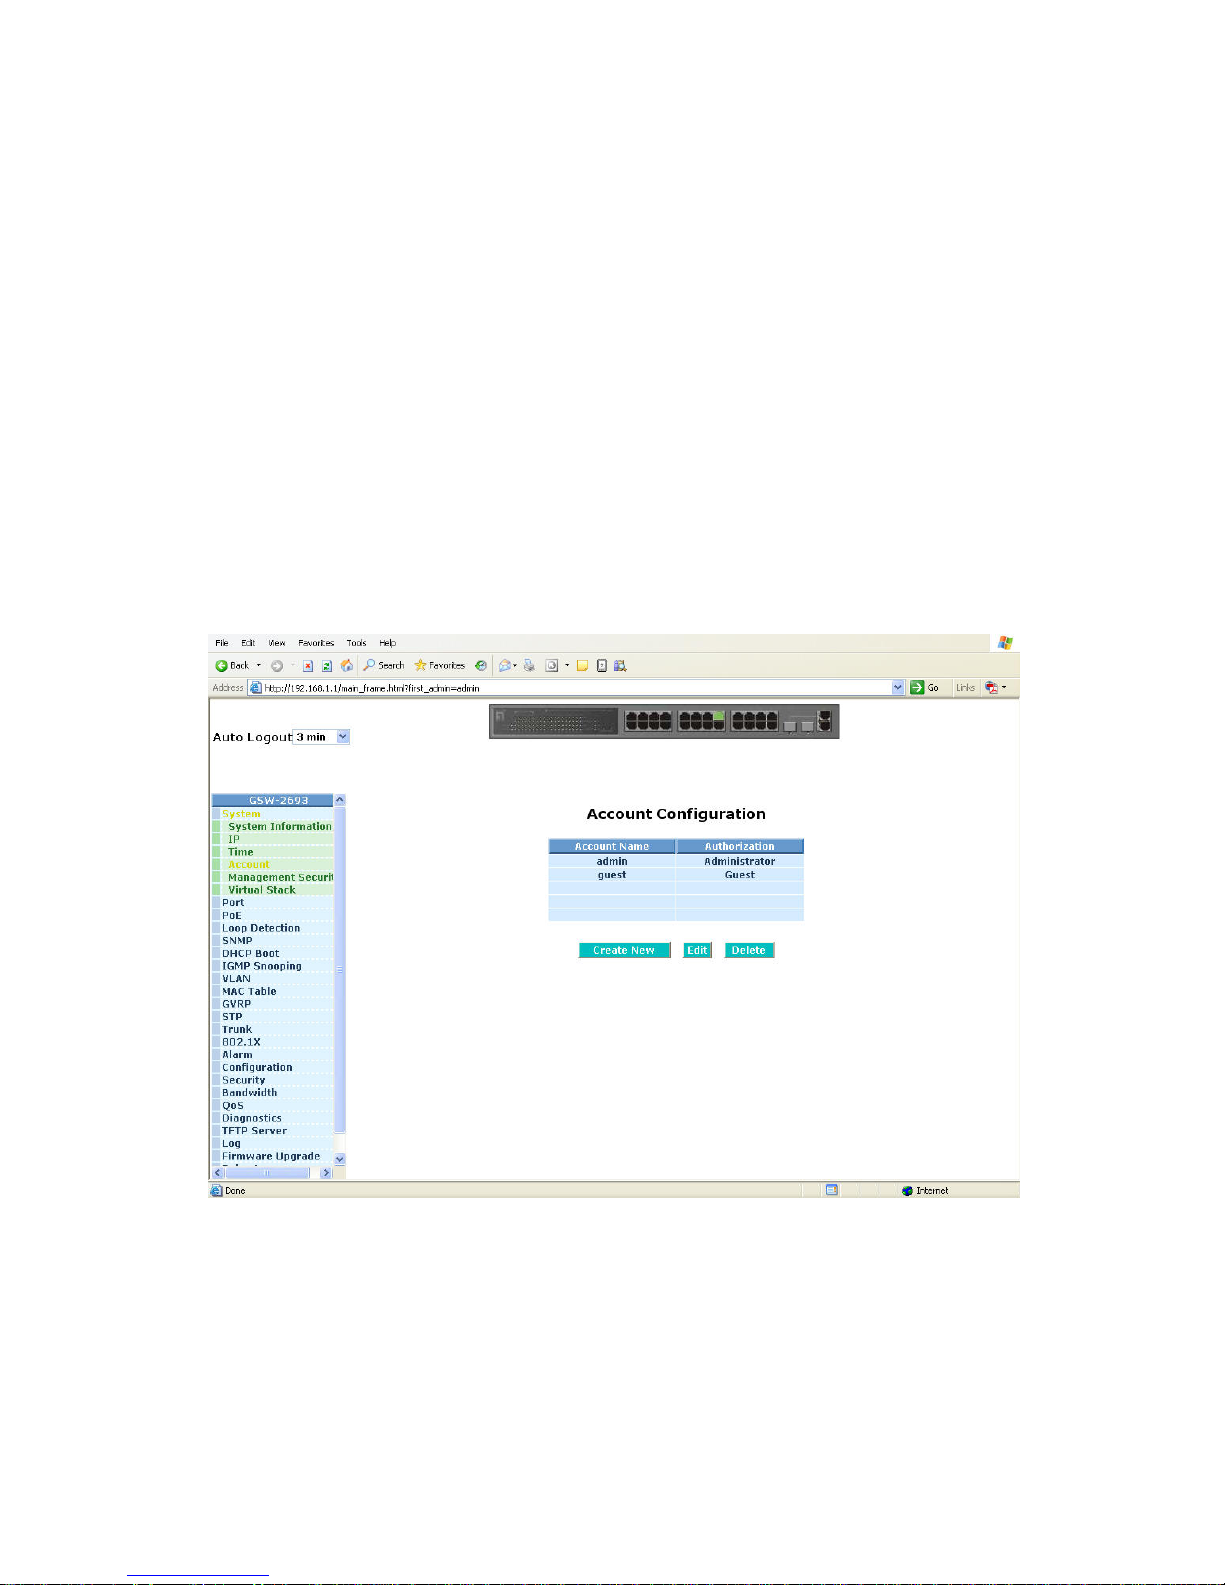
3-1-4. Account Configuration
In this function, only administrator can create, modify or delete the username
and password. Administrator can modify other guest identities’ password without
confirming the password but it is necessary to modify the administrator-equivalent
identity. Guest-equivalent identity can modify his password only. Please note that
you must confirm administrator/guest identity in the field of Authorization in advance
before configuring the username and password. Only one administrator is allowed
to exist and unable to be deleted. In addition, up to 4 guest accounts can be created.
The default setting for user account is:
Username : admin
Password : admin
The default setting for guest user account is:
Username : guest
Password : guest
Fig. 3-6
Page 49
41
3-1-5. Management Security
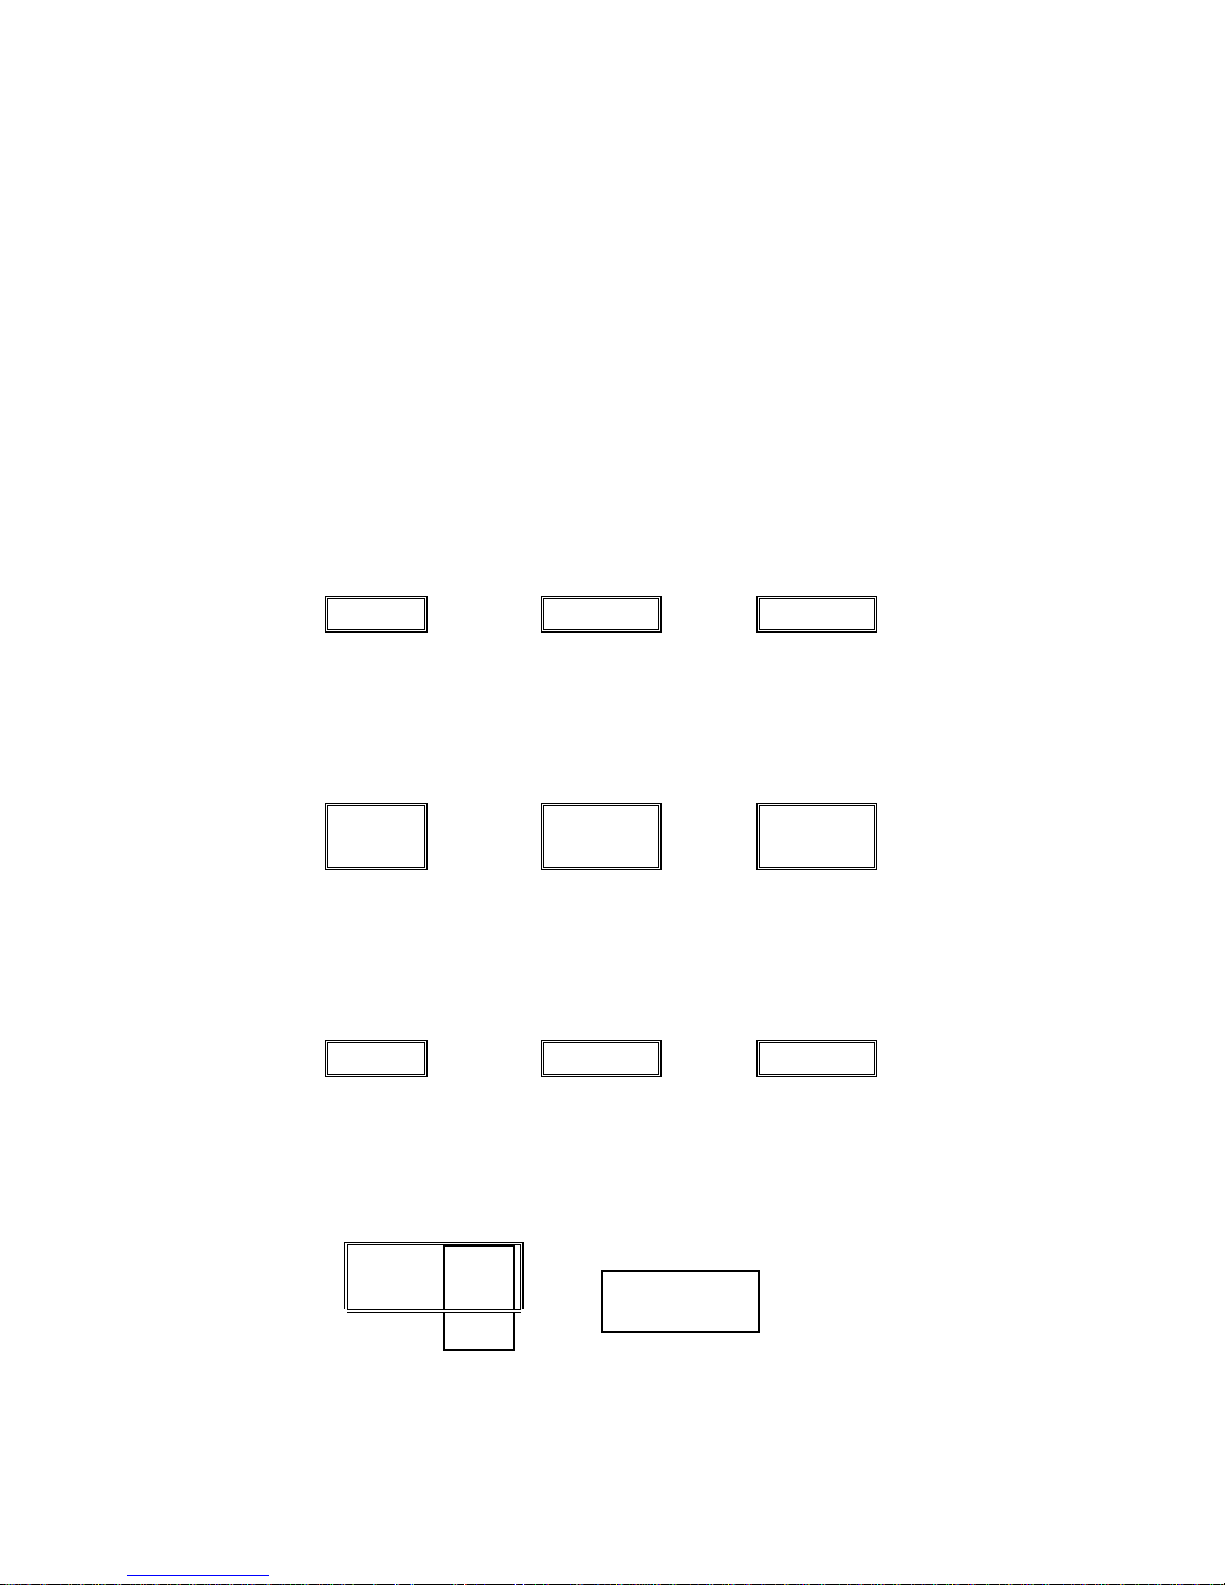
Through the management security configuration, the manager can do the
strict setup to control the switch and limit the user to access this switch.
The following rules are offered for the manager to manage the switch:
Rule 1) : When no lists exists, then it will accept all connections.
Accept
-----------------------------------------------------------------------
Rule 2) : When only “accept lists” exist, then it will deny all connections,
excluding the connection inside of the accepting range.
Accept Deny Accept Deny Accept
-----------------------------------------------------------------------
Rule 3) : When only “deny lists” exist, then it will accept all connections,
excluding the connection inside of the denying range.
Deny Accept Deny
A
ccept
Deny
-----------------------------------------------------------------------
Rule 4) : When both “accept and deny” lists exist, then it will deny all
connections, excluding the connection inside of the accepting range.
Accept Deny Deny Deny Accept
-----------------------------------------------------------------------
Rule 5) : When both “accept and deny” lists exist, then it will deny all
connections, excluding the connection inside of the accepting range and NOT
inside of the denying range at the same time.
Accept
Deny
Deny| Acc | Deny | Acc | Deny
----------------------------------------------------------------------
Accept
Page 50
42
Function name:
Management Security Configuration
Function description:
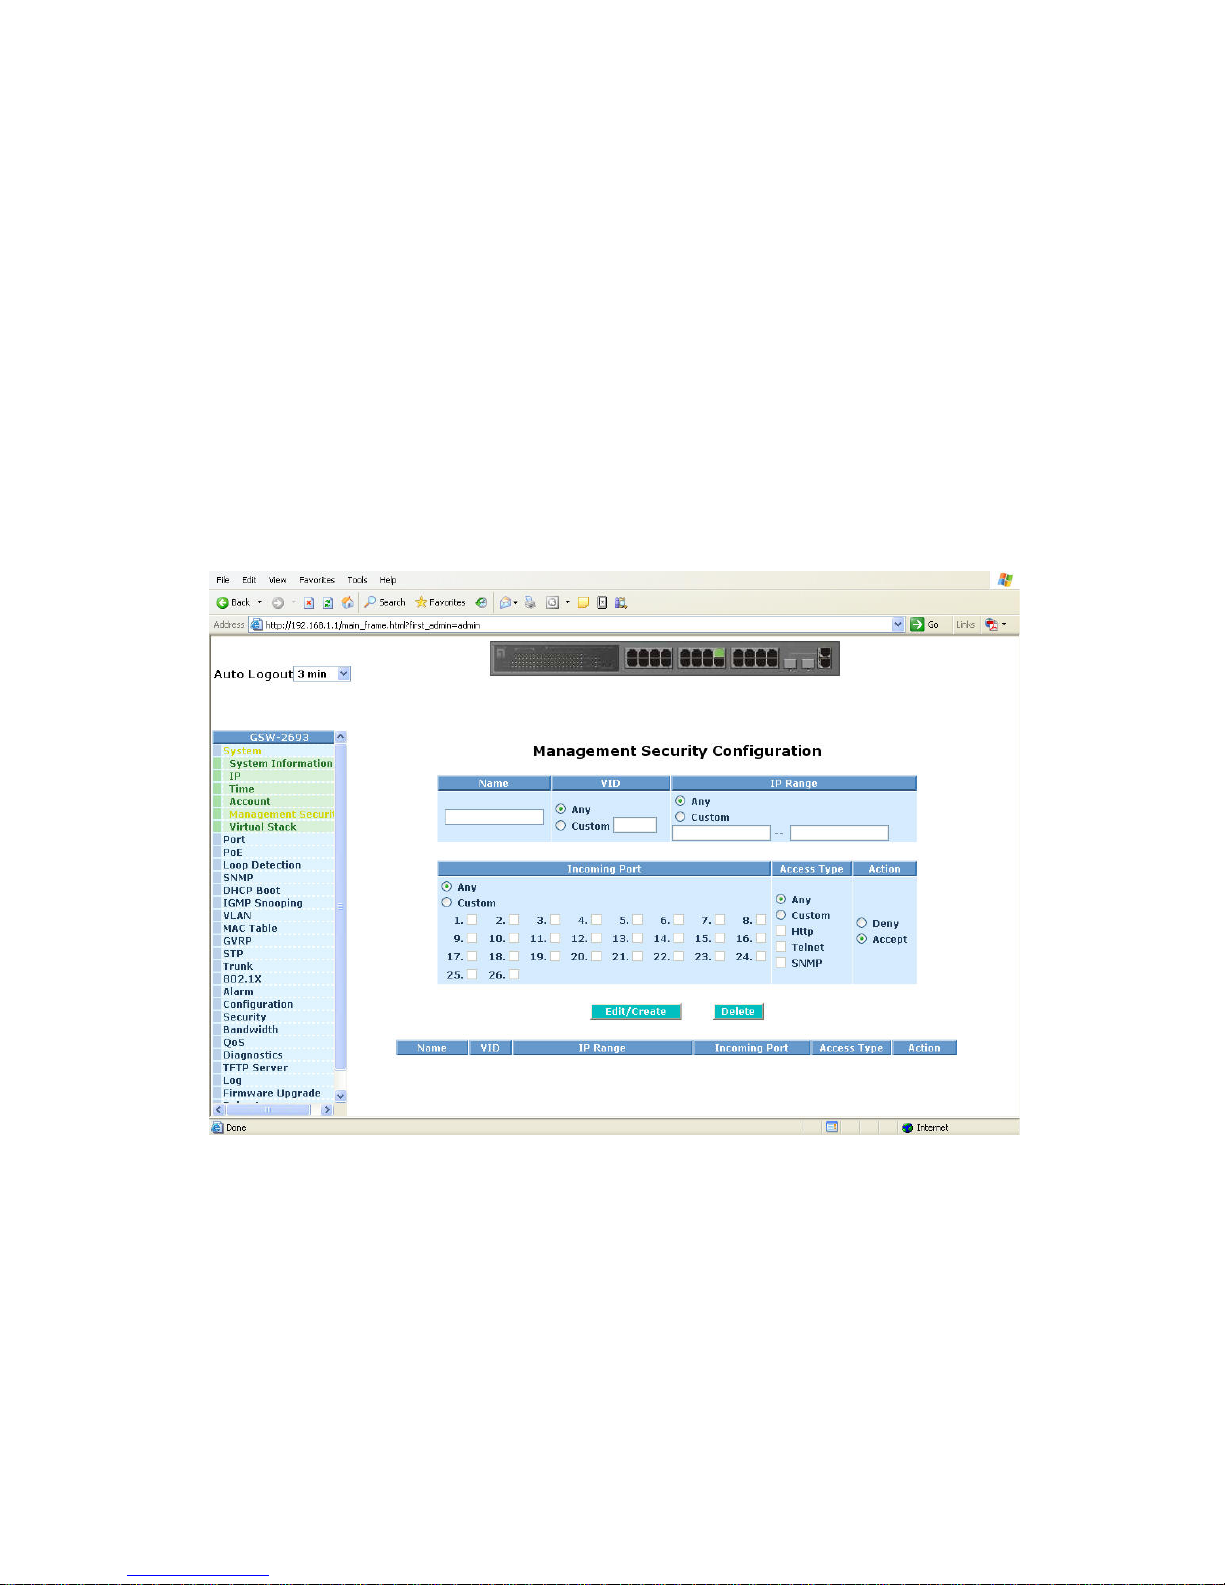
The switch offers Management Security Configuration function. With this
function, the manager can easily control the mode that the user connects to
the switch. According to the mode, users can be classified into two types:
Those who are able to connect to the switch (Accept) and those who are
unable to connect to the switch (Deny). Some restrictions also can be placed
on the mode that the user connect to the switch, for example, we can decide
that which VLAN VID is able to be accepted or denied by the switch, the IP
range of the user could be accepted or denied by the switch, the port that the
user is allowed or not allowed to connect with the switch, or the way of
controlling and connecting to the switch via Http, Telnet or SNMP.
Fig. 3-7
Parameter description:
Name:
A name is composed of any letter (A-Z, a-z) and digit (0-9) with maximal
8 characters.
VID:
The switch supports two kinds of options for managed valid VLAN VID,
including “Any” and “Custom”. Default is “Any”. When you choose
“Custom”, you can fill in VID number. The valid VID range is 1~4094.
Page 51
43
IP Range:
The switch supports two kinds of options for managed valid IP Range,
including “Any” and “Custom”. Default is “Any”. In case that” Custom”
had been chosen, you can assigned effective IP range. The valid range
is 0.0.0.0~255.255.255.255.
Incoming Port:
The switch supports two kinds of options for managed valid Port Range,
including “Any” and “Custom”. Default is “Any”. You can select the ports
that you would like them to be worked and restricted in the management
security configuration if ”Custom” had been chosen.
Access T ype:
The switch supports two kinds of options for managed valid Access Type,
including “Any” and “Custom”. Default is “Any”. “Http”, “Telnet” and
“SNMP” are three ways for the access and managing the switch in case
that” Custom” had been chosen.
Action:
The switch supports two kinds of options for managed valid Action Type,
including “Deny” and “Accept”. Default is “Deny”. When you choose
“Deny” action, you will be restricted and refused to manage the switch
due to the “Access Type” you choose. However, while you select “Accept”
action, you will have the authority to manage the switch.
Edit/Create:
A new entry of Management Security Configuration can be created after
the parameters as mentioned above had been setup and then press
<Edit/Create> button. Of course, the existed entry also can be modified
by pressing this button.
Delete:
Remove the existed entry of Management Security Configuration from
the management security table.
Page 52
44
3-1-6. Virtual Stack
Function name:
Virtual Stack
Function description:
Virtual Stack Management(VSM) is the group management function. Through
the proper configuration of this function, switches in the same LAN will be
grouped automatically. And among these switch, one switch will be a master
machine, and the others in this group will become the slave devices.
VSM offers a simple centralized management function. It is not necessary to
remember the address of all devices, manager is capable of managing the
network with knowing the address of the Master machine. Instead of SNMP
or Telnet UI, VSM is only available in Web UI. While one switch become the
Master, two rows of buttons for group d evice will appear on the top of its Web
UI. By pressing these buttons, user will be allowed to connect the Web UI of
the devices of the group in the same window without the login of these device.
The most top-left button is only for Master device(See Fig.3-8). The
background color of the button you press will be changed to represent that
the device is under your management.
Note: It will remove the grouping temporarily in case that you login the switch
via the console.
The device of the group will be shown as station address ( the last number of
IP Address) + device name on the button (e.g. 196_GSW-2693), otherwise it
will show ” ---- “ if no corresponding device exists.
Once the devices join the group successfully, then they are merely able to be
managed via Master device, and user will fail to manage them via
telnet/console/web individually.
Up to 16 devices can be grouped for VSM, however, only one Master is
allowed to exist in each group. For Master redundancy, user may configure
more than two devices as Master device, however, the Master de vice with the
smaller MAC value will be the Master one. All of these 16 devices can
become Master device and back up with each other .
Page 53
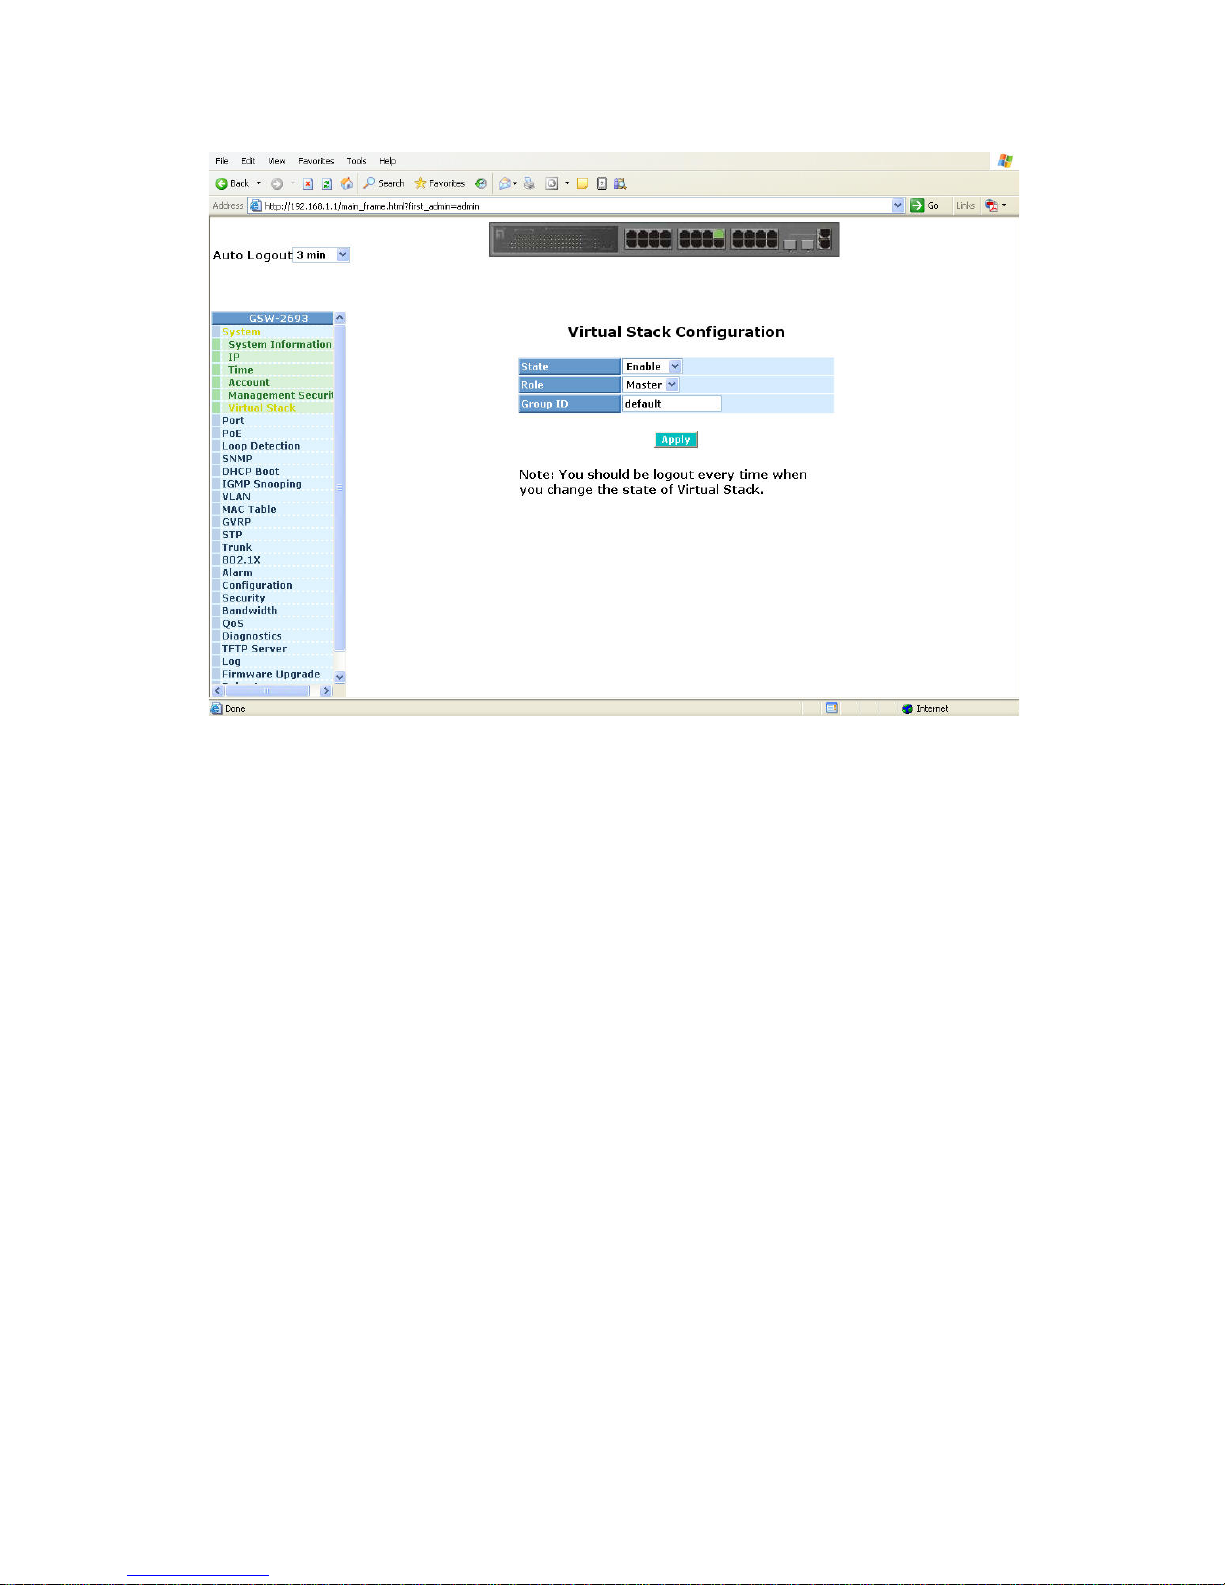
45
Fig. 3-8
Parameter description:
St ate:
It is used for the activation or de-activation of VSM. Default is Enable.
Role:
The role that the switch would like to play in virtual stack. Two types of
roles, including master and slave are offered for option. Default is Maste r.
Group ID:
It is the group identifier (GID) which signs for VSM. Valid letters are A-Z,
a-z, 0-9, “
- “ and “_” characters. The maximal length is 15 characters.
Page 54
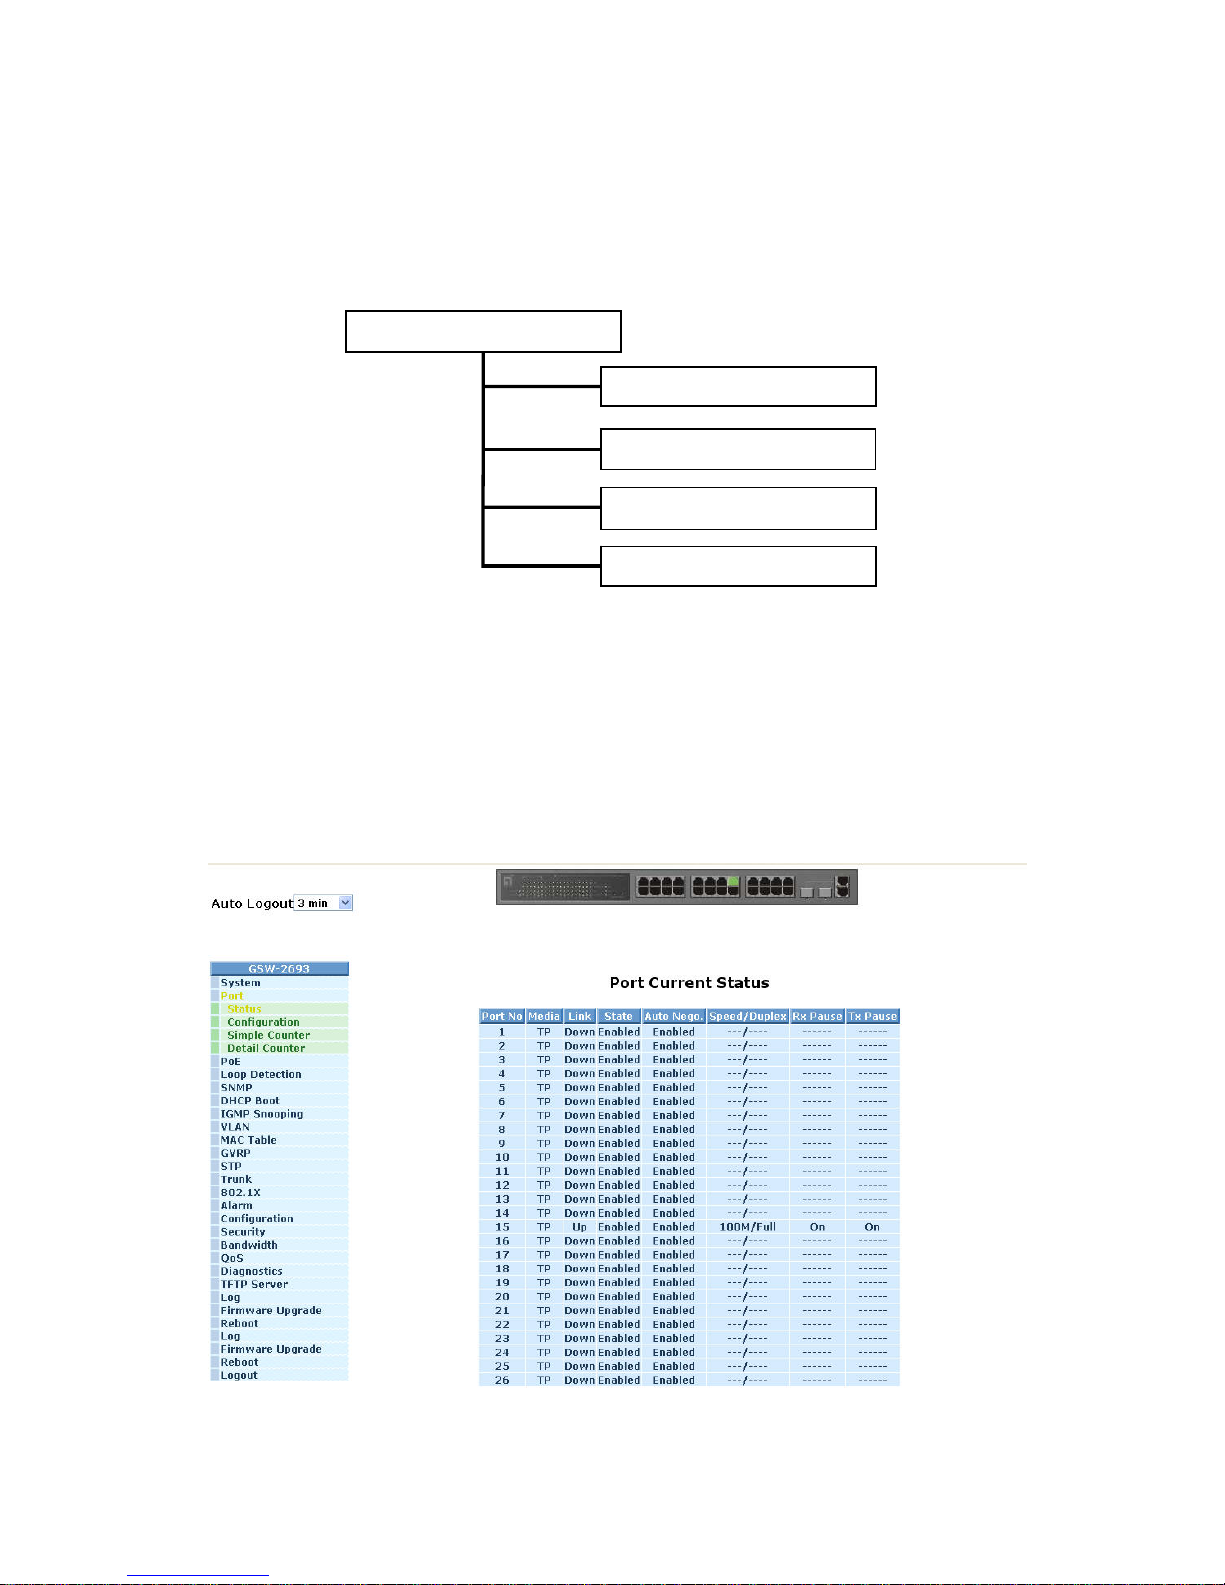
46
3-2. Port Configuration
Four functions, including Port Status, Port Configuration, Simple Counter and
Detail Counter are contained in this function folder for port monitor and
management. Each of them will be described in detail orderly in the following
sections.
3-2-1.Port Status
The function Port Status gathers the information of all ports’ current status
and reports it by the order of port number, media, link status, port state, AutoNegotiation status, speed/duplex, Rx Pause and Tx Pause. An extra media type
information for the module ports 25 and 26 is also offered (See Fig. 3-11).
Fig. 3-10
Status
Configuration
Simple Counter
Detail Counter
Port Configuration
Page 55
47
Function name:
Port Status
Function Description:
Report the latest updated status of all ports in this switch. When any one of the ports in
the switch changes its parameter displayed in the page, it will be automatically
refreshed the port current status about every 5 seconds.
Parameter Descriptio n:
Port No:
Display the port number. The number is 1 – 26. Both port 25 and 26 are
optional modules.
Media:
Show the media type adopted in all ports. The Port 25 and Port 26 are
optional modules, which support either fiber or UTP media with either
Gigabit Ethernet (1000Mbps) or 10/100Mbps Fast Ethernet port. They
may have different media types and speed. Especially, fiber port has
comprehensive types of connector, distance, fiber mode and so on. The
switch describes the module ports with the following page.
Link:
Show that if the link on the port is active or not. If the link is connected to
a working-well device, the Link will show the link “Up”; otherwise, it will
show “Down”. This is determined by the hardware on both devices of the
connection.
No default value.
St ate:
Show that the communication function of the port is “Enabled” or
“Disabled”. When it is enabled, traffic can be transmitted and received via
this port. When it is disabled, no traffic can be transferred through this
port. Port State is configured by user.
Default: Enabled.
Auto Nego.:
Show the exchange mode of Ethernet MAC. There are two modes
supported in the switch. They are auto-negotiation mode “Enabled” and
forced mode “Disabled”. When in “Enabled” mode, this function will
automatically negotiate by hardware itself and exchange each other the
capability of speed and duplex mode with other site which is linked, and
comes out the best communication way. When in “Disabled” mode, both
parties must have the same setting of speed and duplex, otherwise, both
of them will not be linked. In this case, the link result is “Down”.
Default: Enabled
Page 56
48
Speed / Duplex :
Display the speed and duplex of all port. There are three speeds 10Mbps,
100Mbps and 1000Mbps supported for TP media, and the duplex
supported is half duplex and full duplex. If the media is 1Gbps fiber, it is
1000Mbps supported only. The status of speed/duplex mode is
determined by 1) the negotiation of both local port and link partner in
“Auto Speed” mode or 2) user setting in “Force” mode. The local port has
to be preset its capability.
In port 1 – 24, they are supported Fast Ethernet with TP media only, so
the result will show 100M/Full or 100M/Half, 10M/Full and 10M/Half
duplex.
In port 25 and port 26, if the media is 1000Mbps with TP media, it will
show the combinations of 10/100M and Full/Half duplex, 1000Mbps and
Full duplex only. If the media is 1000Mbps with fiber media, it will show
only 1000M/Full duplex.
Default: None, depends on the result of the negotiation.
Rx Pause:
The way that the port adopts to process the PAUSE frame. If it shows
“on”, the port will care the PAUSE frame; otherwise, the port will ignore
the PAUSE frame.
Default: None
Tx Pause:
It decides that whether the port transmits the PAUSE frame or not. If it
shows “on”, the port will send PAUSE frame; otherwise, the port will not
send the PAUSE frame.
Default: None
Page 57
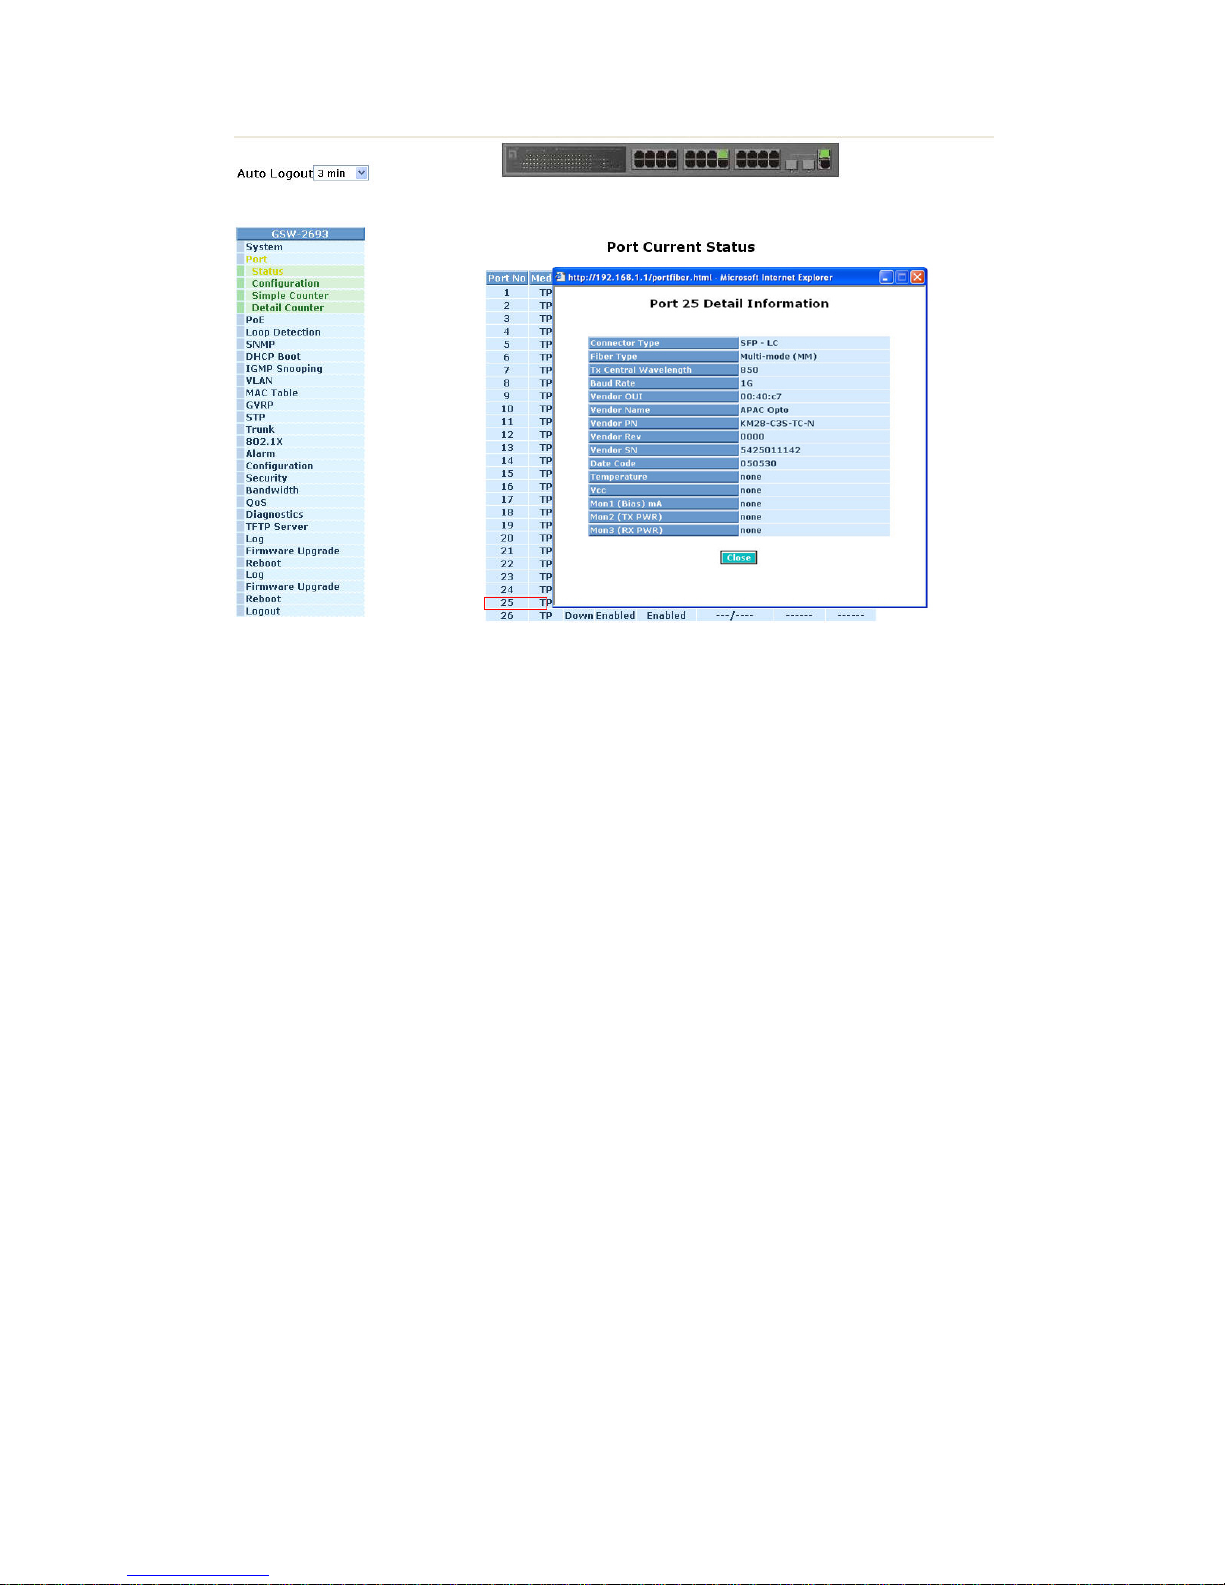
49
Fig. 3-11
Parameter description of Port 25 and Port 26:
Connector Type:
Display the connector type, for instance, UTP, SC, ST, LC and so
on.
Fiber Typ e:
Display the fiber mode, for instance, Multi-Mode, Single-Mode.
Tx Central Wavelength:
Display the fiber optical transmitting central wavelength, for
instance, 850nm, 1310nm, 1550nm and so on.
Baud Rate:
Display the maximum baud rate of the fiber module supported, for
instance, 10M, 100M, 1G and so on.
Vendo r OUI:
Display the Manufacturer's OUI code which is assigned by IEEE.
Vendo r Name:
Display the company name of the module manufacturer.
Vendo r P/N:
Display the product name of the naming by module manufacturer.
Vendor Rev (Revision):
Display the module revision.
Page 58
50
Vendor SN (Serial Number):
Show the serial number assigned by the manufacturer.
Date Code:
Show the date this module was made.
Temperature:
Show the current temperature of module.
Vcc:
Show the working DC voltage of module.
Mon1(Bias) mA:
Show the Bias current of module.
Mon2(TX PWR):
Show the transmit power of module.
Mon3(RX PWR):
Show the receiver power of module.
Note:
User can click on plugged SFP port for Detail Information which
shows on top of diagram.
Page 59
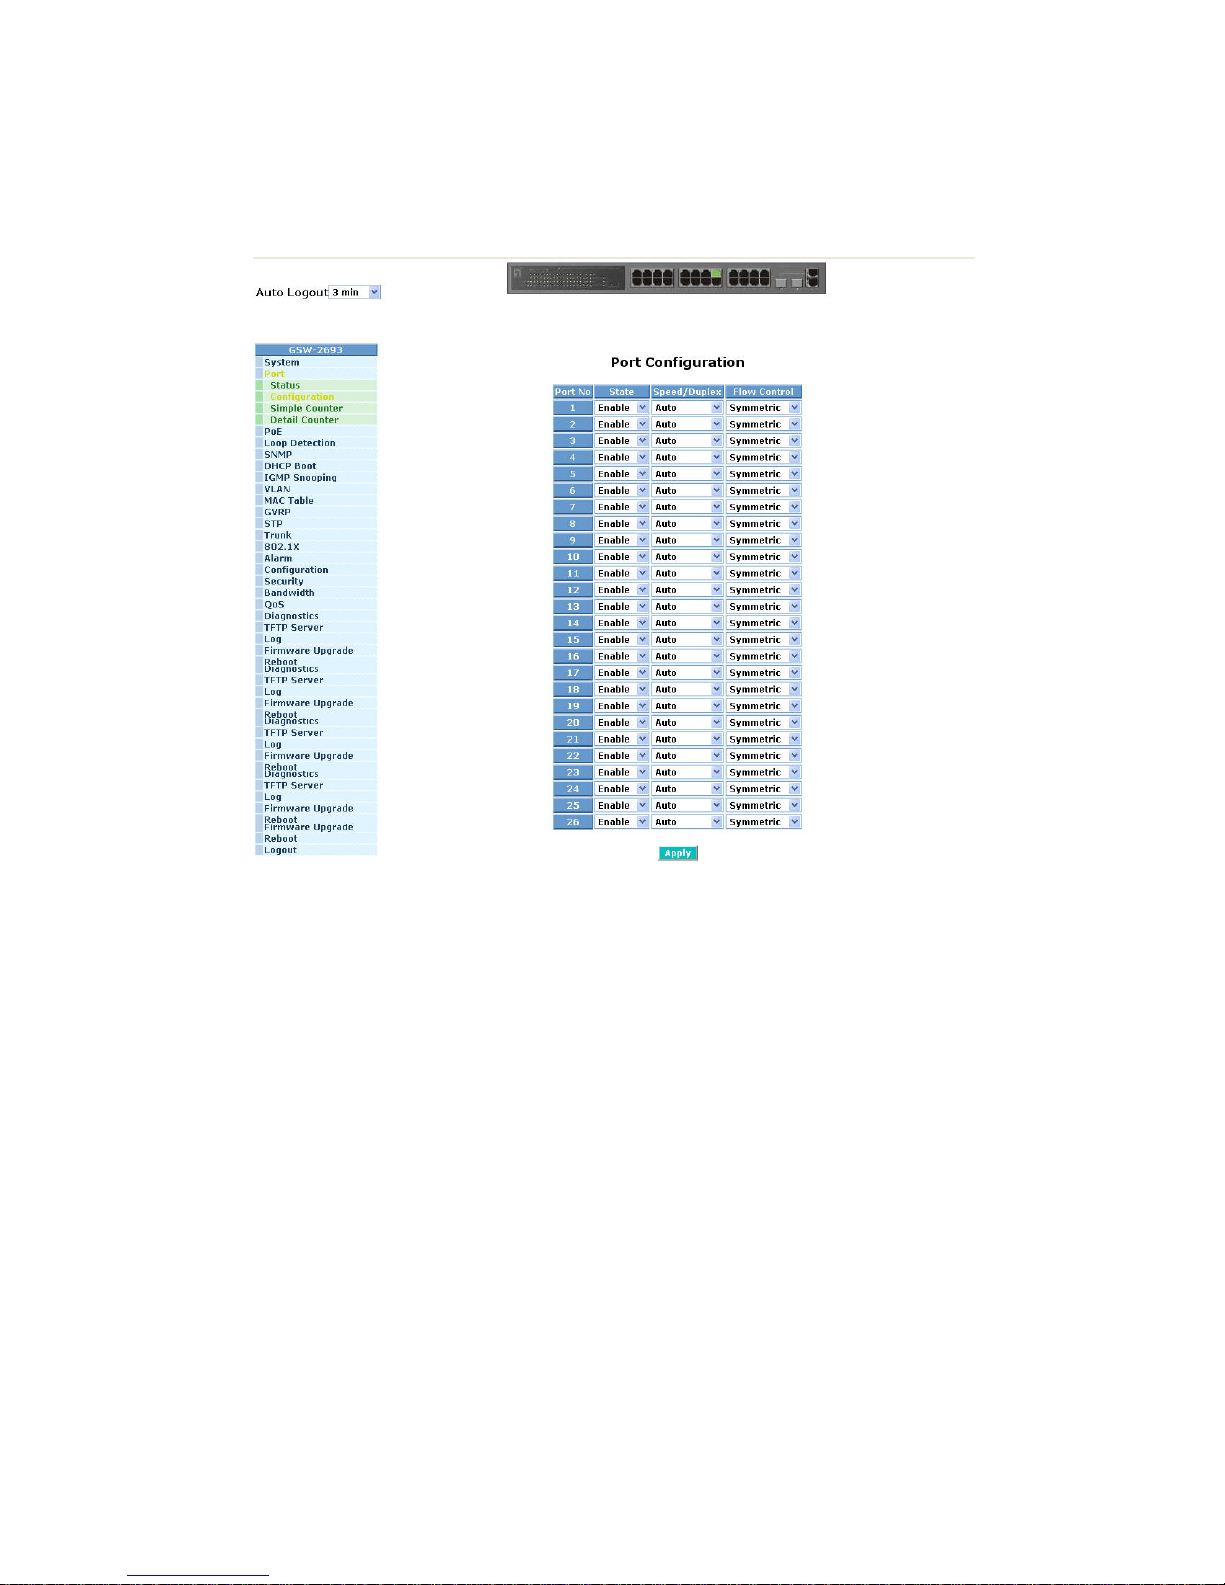
51
3-2-2. Port Configuration
Port Configuration is applied to change the setting of each port. In this
configuration function, you can set/reset the following functions. All of them are
described in detail below.
Fig. 3-12
Function name:
Port Configuration
Function description:
It is used to set each port’s operation mode. The switch supports 3
parameters for each port. They are State, Speed/Duplex and Flow Control.
Parameter description:
St ate:
Set the communication capability of the port is Enabled or Disabled.
When enabled, traffic can be transmitted and received via this port.
When disabled, the port is blocked and no traffic can be transferred
through this port. Port State is configurable by the user. There are only
two states “Enable” and “Disable” able to choose. If you set a port’s state
“Disable”, then that port is prohibited to pass any traffic, even it looks
Link up.
Default: Enable.
Page 60
52
Speed/Duplex:
Set the speed and duplex of the port. In speed, 10/100Mbps baud rate is
available for Fast Ethernet, Gigabit module in port 25, 26. If the media is
1Gbps fiber, it is always 1000Mbps and the duplex is full only. If the
media is TP, the Speed/Duplex is comprised of the combination of speed
mode, 10/100/1000Mbps, and duplex mode, full duplex and half duplex.
The following table summarized the function the media supports.
Media type NWay Speed Duplex
100M TP ON/OFF 10/100M Full/Half
1000M TP ON/OFF 10/100/1000M Full for all, Half for 10/100
1000M Fiber ON/OFF 1000M Full
In Auto-negotiation mode, no default value. In Forced mode, default
value depends on your setting.
Flow Control:
There are two modes to choose in flow control, including Symmetric and
Asymmetric. If flow control is set Symmetric, both parties can send
PAUSE frame to the transmitting device(s) if the receiving port is too
busy to handle. When it is set Asymmetric, this will let the receiving port
care the PAUSE frame from transmitting device(s), but it doesn’t send
PAUSE frame. This is one-way flow control.
Default: Symmetric.
Page 61
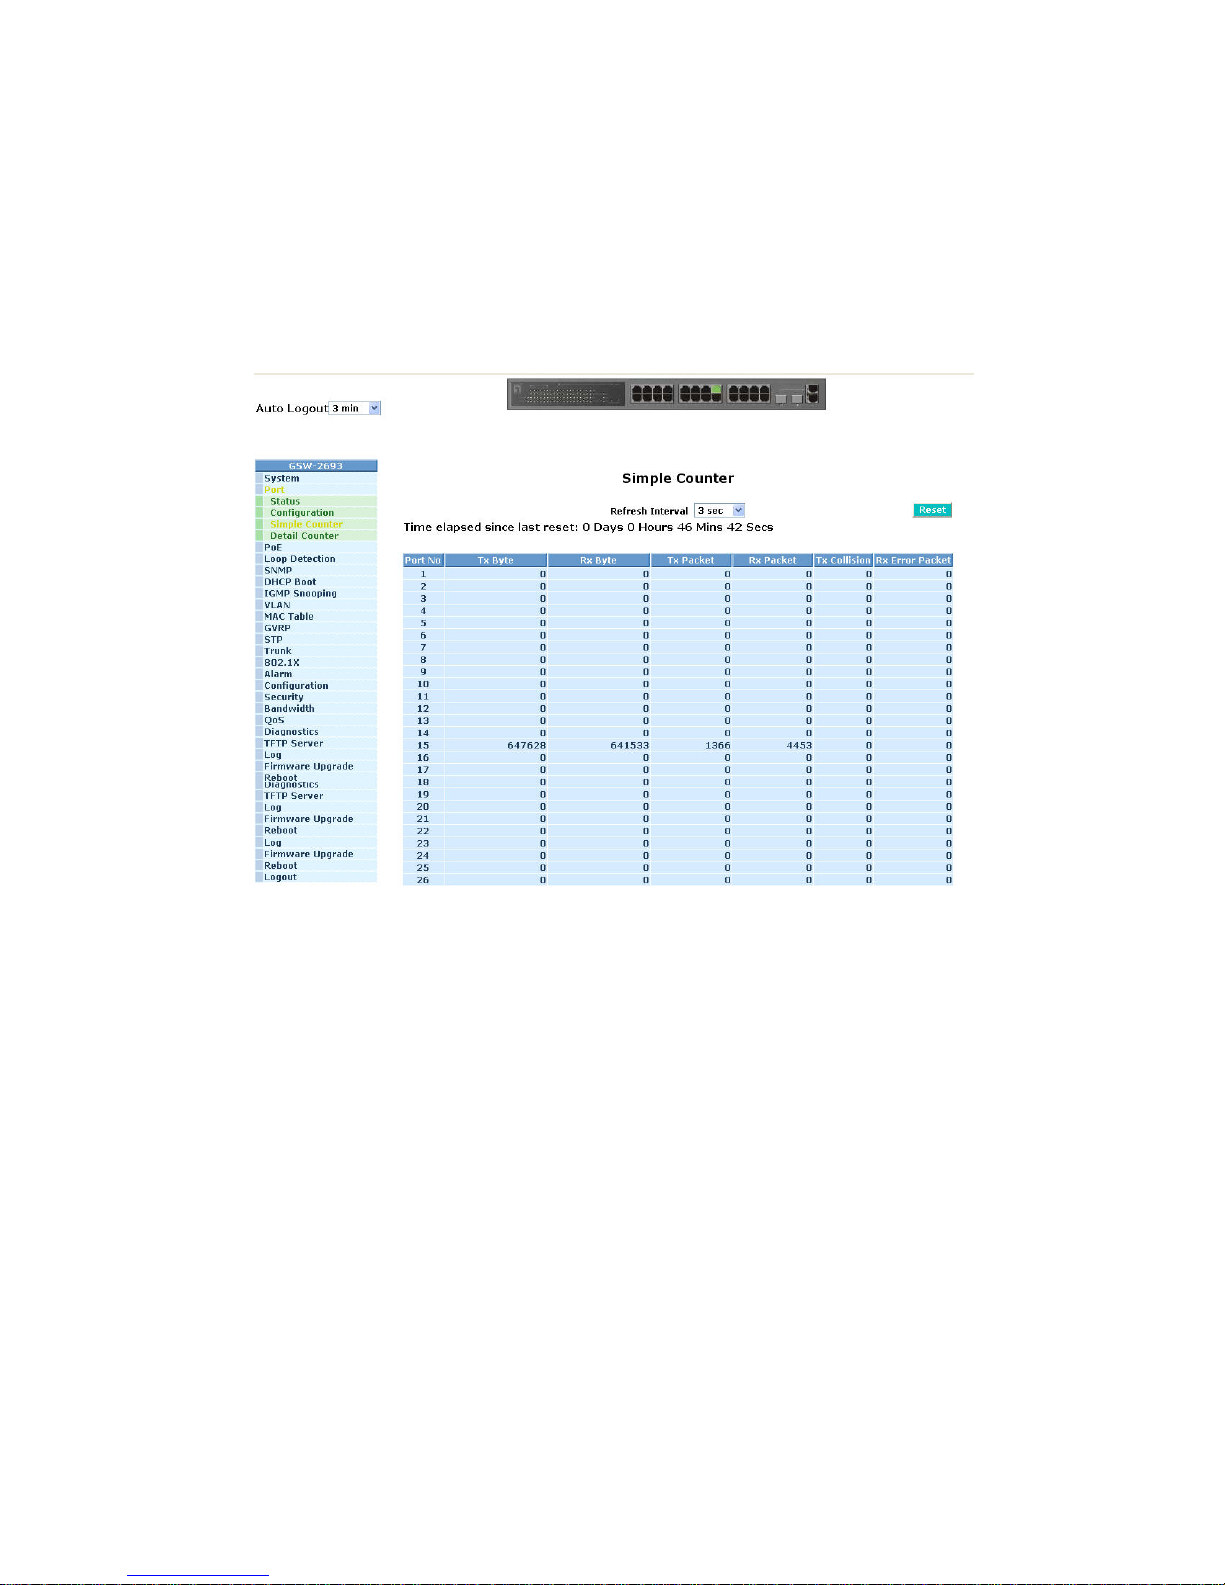
53
3-2-3. Simple Counter
The function of Simple Counter collects any information and provides the
counting about the traffic of the port, no matter the packet is good or bad.
In the Fig. 3-10, the window can show all ports’ counter information at the
same time. Each data field has 20-digit long. If the counting is overflow, the counter
will be reset and restart counting. The data is updated every time interval defined by
the user. The valid range is 3 to 10 seconds. The Refresh Interval is used to set the
update frequency. Default update time is 3 seconds.
Fig. 3-13
Function name:
Simple Counter
Function description:
Display the summary counting of each port’s traffic, including Tx Byte, Rx Byte,
Tx Packet, Rx Packet, Tx Collision and Rx Error Packet.
Parameters description:
Tx Byte:
Total transmitted bytes.
Rx Byte:
Total received bytes.
Tx Packet:
The counting number of the packet transmitted.
Page 62
54
Rx Packet:
The counting number of the packet received.
Tx Collision:
Number of collisions transmitting frames experienced.
Rx Error Packet:
Number of bad packets received.
Page 63
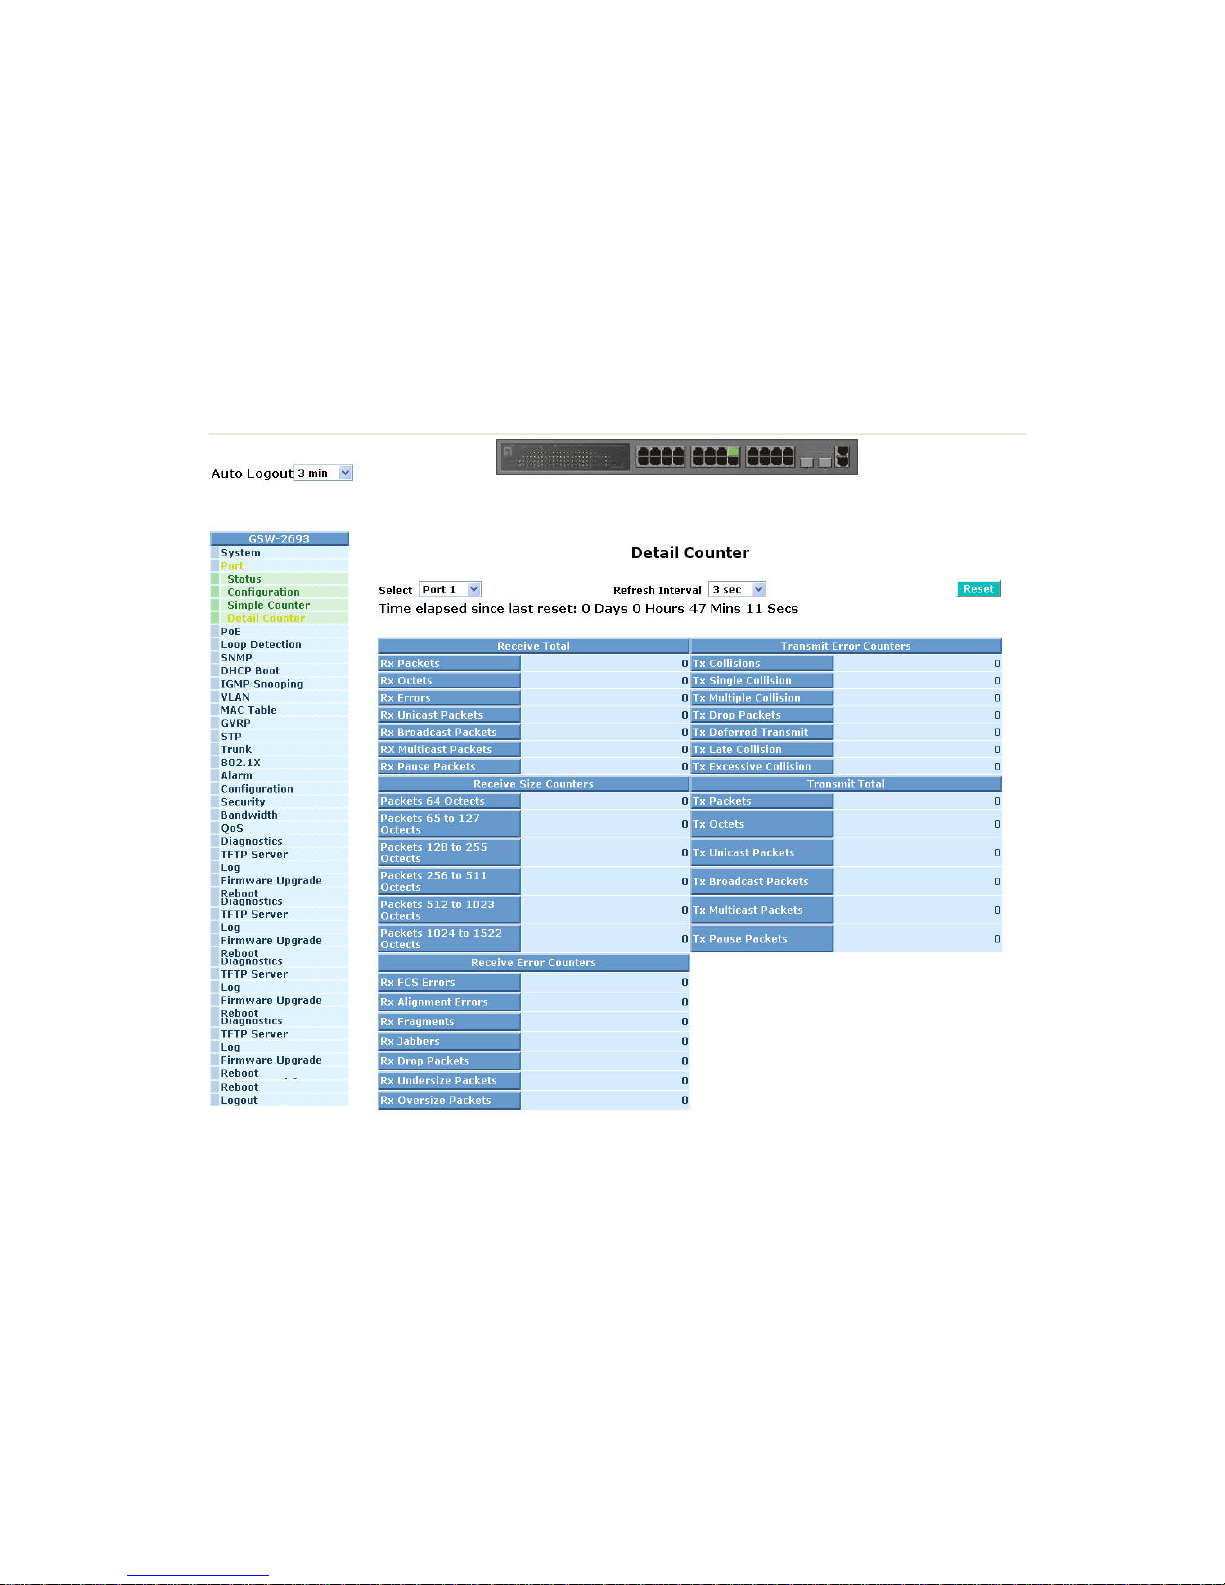
55
3-2-4. Detail Counter
The function of Detail Counter collects any information and provides the
counting about the traffic of the port, no matter the packet is good or bad.
In the Fig. 3-14, the window can show only one port counter information at
the same time. To see another port’s counter, you have to pull down the list of
Select, then you will see the figures displayed about the port you had chosen.
Each data field has 20-digit long. If the counting is overflow, the counter will
be reset and restart counting. The data is updated every time interval defined by the
user. The valid range is 3 to 10 seconds. The Refresh Interval is used to set the
update frequency. Default update time is 3 seconds.
Fig. 3-14
Function name:
Detail Counter
Function description:
Display the detailed counting number of each port’ s traffic. In the Fig. 3-14, the
window can show all counter information of each port at one time.
Page 64
56
Parameter description:
Receive Total
Rx Packets:
The counting number of the packet received.
Rx Octets:
Total received bytes.
Rx Errors:
Number of bad packets received.
Rx Unicast Packets:
Show the counting number of the received unicast packet.
Rx Broadcast Packets:
Show the counting number of the received broadcast packet.
Rx Multicast Packets:
Show the counting number of the received multicast packet.
Rx Pause Packets:
Show the counting number of the received pause packet.
Transmit Error Counters
Tx Collisions:
Number of collisions transmitting frames experienced.
Tx Single Collision:
Number of frames transmitted that experienced exactly one collision.
Tx Multiple Collision:
Number of frames transmitted that experienced more than one collision.
Tx Drop Packets:
Number of frames dropped due to excessive collision, late collision, or
frame aging.
Tx Deferred Transmit:
Number of frames delayed to transmission due to the medium is busy.
Tx Late Collision:
Number of times that a collision is detected later than 512 bit-times into
the transmission of a frame.
Tx Excessive Collision:
Number of frames that are not transmitted because the frame
experienced 16 transmission attempts.
Page 65
57
Receive Size Counters
Packets 64 Octets:
Number of 64-byte frames in good and bad packets received.
Packets 65-127 Octets:
Number of 65 ~ 127-byte frames in good and bad packets received.
Packets 128-255 Octets:
Number of 128 ~ 255-byte frames in good and bad packets received.
Packets 256-511 Octets:
Number of 256 ~ 511-byte frames in good and bad packets received.
Packets 512-1023 Octets:
Number of 512 ~ 1023-byte frames in good and bad packets received.
Packets 1024- 1522 Octets:
Number of 1024-1522-byte frames in good and bad packets received.
Transmit Total
Tx Packets:
The counting number of the packet transmitted.
TX Octets:
Total transmitted bytes.
Tx Unicast Packets:
Show the counting number of the transmitted unicast packet.
Tx Broadcast Packets:
Show the counting number of the transmitted broadcast packet.
Tx Multicast Packets:
Show the counting number of the transmitted multicast packet.
Tx Pause Packets:
Show the counting number of the transmitted pause packet.
Receive Erro Counters
Rx FCS Errors:
Number of bad FSC packets received.
Rx Alignment Errors:
Number of Alignment errors packets received.
Rx Fragments:
Number of short frames (< 64 bytes) with invalid CRC.
Rx Jabbers:
Number of long frames(according tomax_length register) with invalid
CRC.
Rx Drop Packets:
Frames dropped due to the lack of receiving buffer.
Rx Undersize Packets:
Number of short frames (<64 Bytes) with valid CRC.
Rx Oversize Packets:
Number of long frames(according to max_length register) with valid CRC.
Page 66
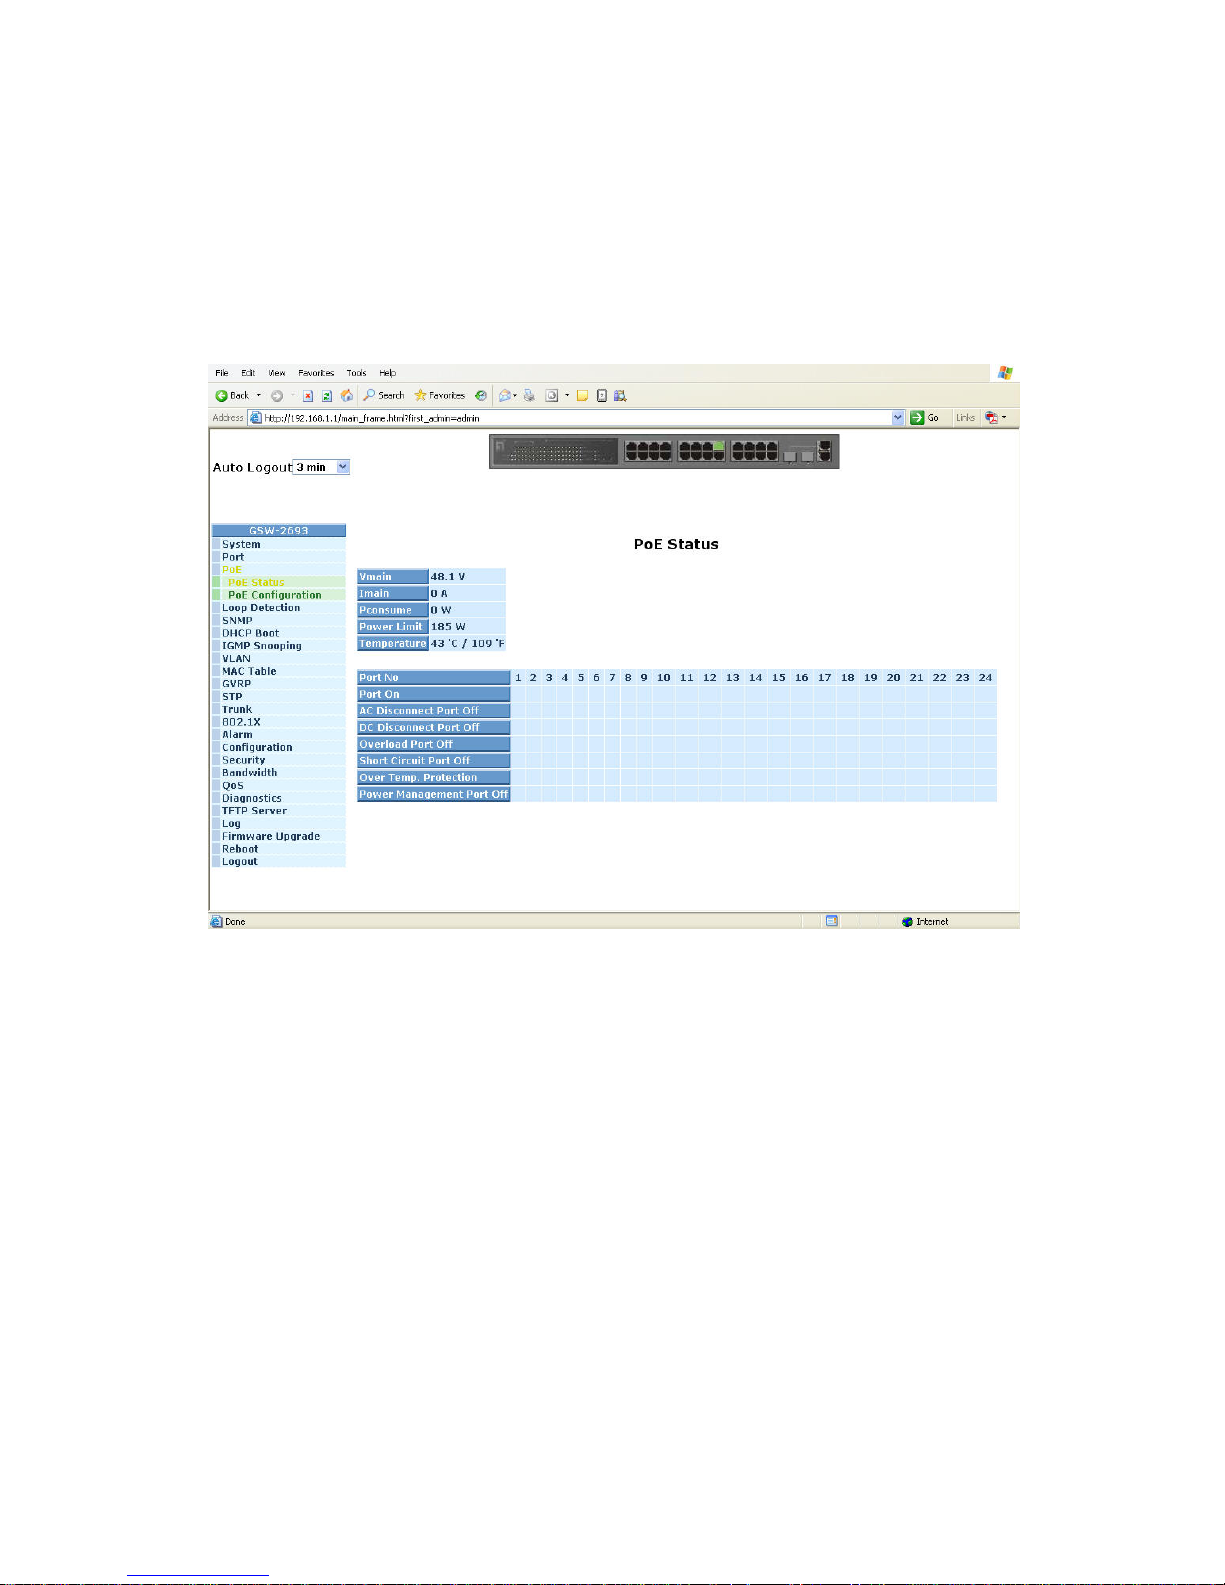
58
3-3. PoE
Function name:
PoE Status
Function description:
Display the information about the PoE status.
Fig. 3-15
Parameter description:
Vmain:
The volt is supplied by the PoE.
Imain:
The sum of the current that every port supplies.
Pconsume:
The sum of the power that every port supplies.
Power Limit:
The maximal power that the switch can supply (Read Only).
Temperature:
The temperature of the chip on PoE.
Page 67
59
Port No:
Port number.
Port On:
Show whether the port is supplying the power to the PD or not.
AC Disconnect Port Off:
Port is turned off due to the AC Disconnect function.
DC Disconnect Port Off:
Port is turned off due to the DC Disconnect function.
Overload Port Off:
The switch will stop supplying the power to the port due to the power
required by the PD that is linked to the port on the switch excesses the
Class setting of the PD.
Short Circuit Port Off:
The switch will stop supplying the power to the port if it detects that the
PD linked to the port is short circuit.
Over Temp. Protection:
The port of the switch will be disabled due to fast transient rise in
temperature to 240
o
C or slow rise in temperature to 200oC.
Power Management Port Off:
Due to total power required by all PDs linked to the switch excesses the
power limit, so the switch stops supplying the power to this port after
referring to the information of the priority.
Page 68
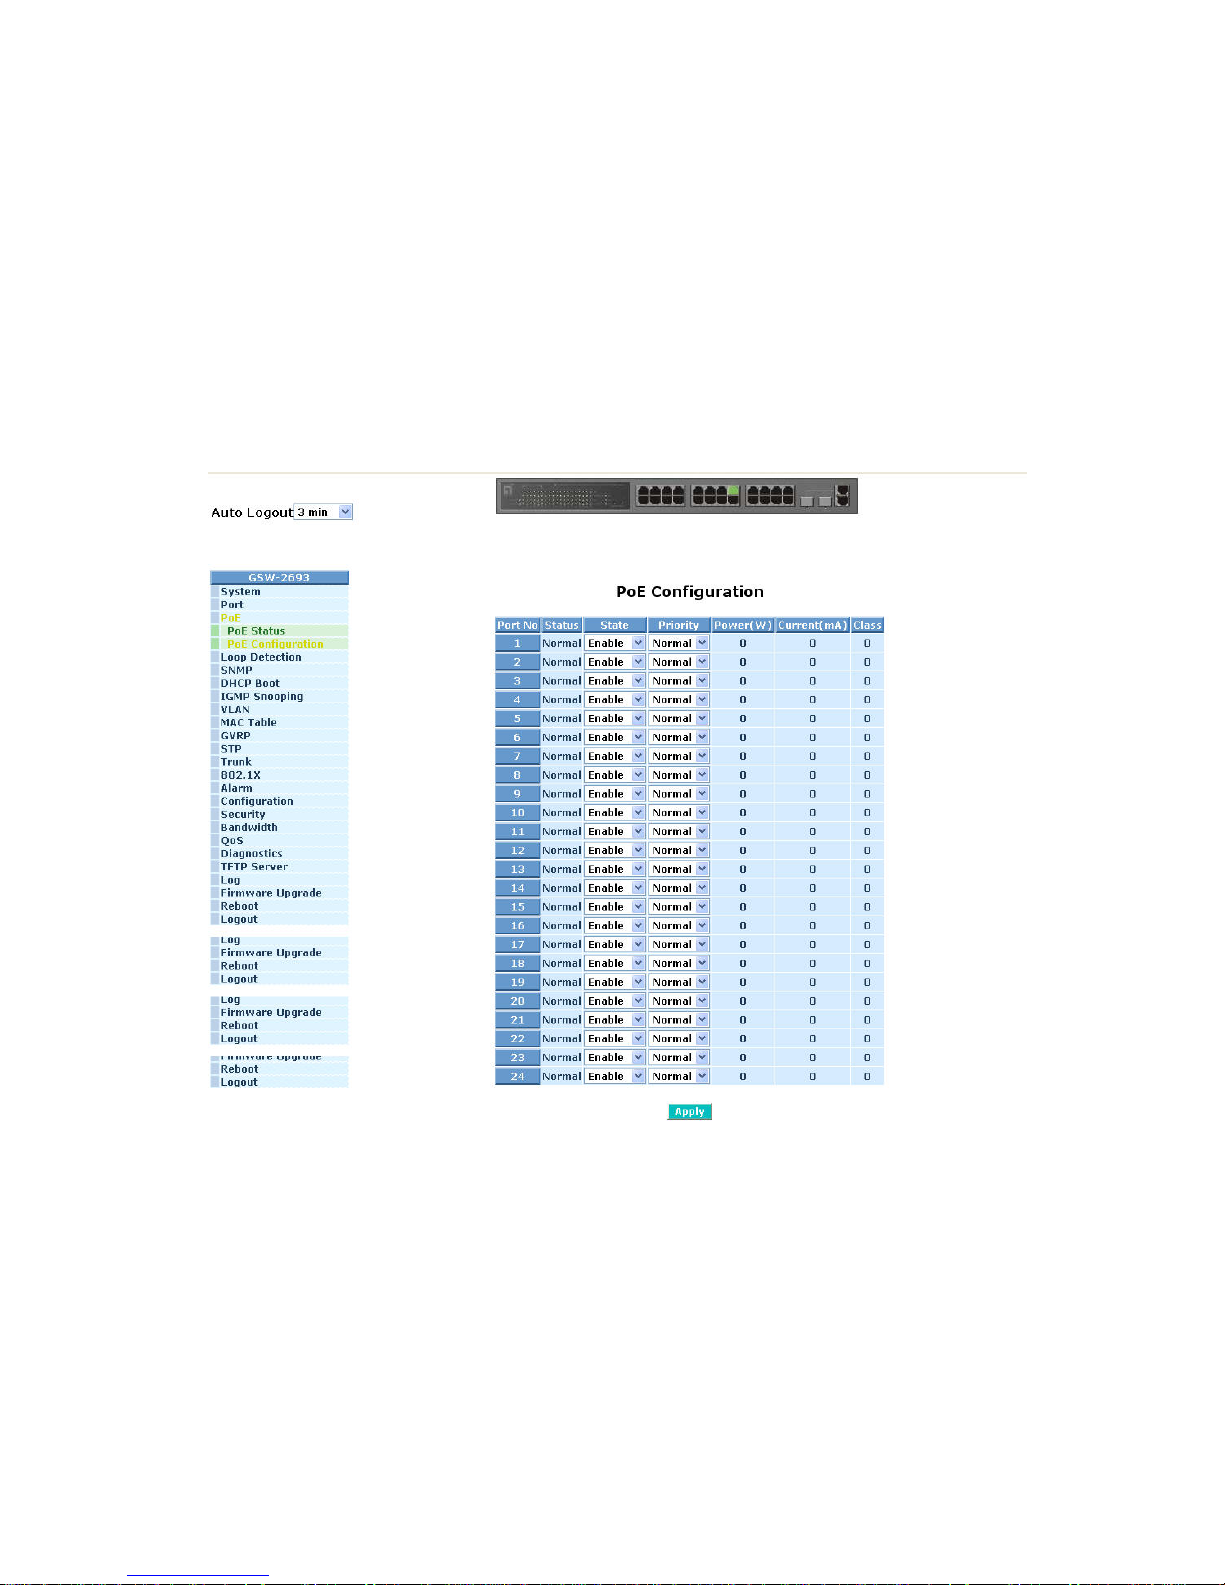
60
Function name:
PoE Configuration
Function description:
In PoE Port Management function, user can configure the settings about PoE.
The switch complies with IEEE 802.3af protocol and be capable of detecting
automatically that whether the device linked to the port on the switch is PD
(Powered Device) or not. The switch also manage the power supplement
based on the Class of the PD, and it will stop supplying the power once the
power required by the PD excesses the Class, Short Circuit or over
temperature occurs.
Fig. 3-16
Parameter description:
Status:
Include “Normal” or “Active” two kinds of status. The former means the
port is ready to link and supply the power to the PD at any time. The
latter means the port is in the condition of supplying the power.
State:
“Enable” means the manager allows the power supplied to the PD is
legal while the port linked to the PD; “Disable” means the port does not
own PoE function.
Page 69
61
Priority:
Three options are offered for the user to choose, including Normal, Low
and High. Default is Normal. The switch will stop supplying the power to
the port based on the order of the priority LowÆNormalÆHigh in case
total power required by all PDs linked to the switch excesses the power
limit. As the ports have the same priority, then the switch will cease the
power supplement from the port with the highest port id (12Æ1).
Power(W):
The power is consumed by the port.
Current(mA):
The current is supplied to the PD by the port.
Class:
The Class of the PD linked to the port of the switch.
Page 70
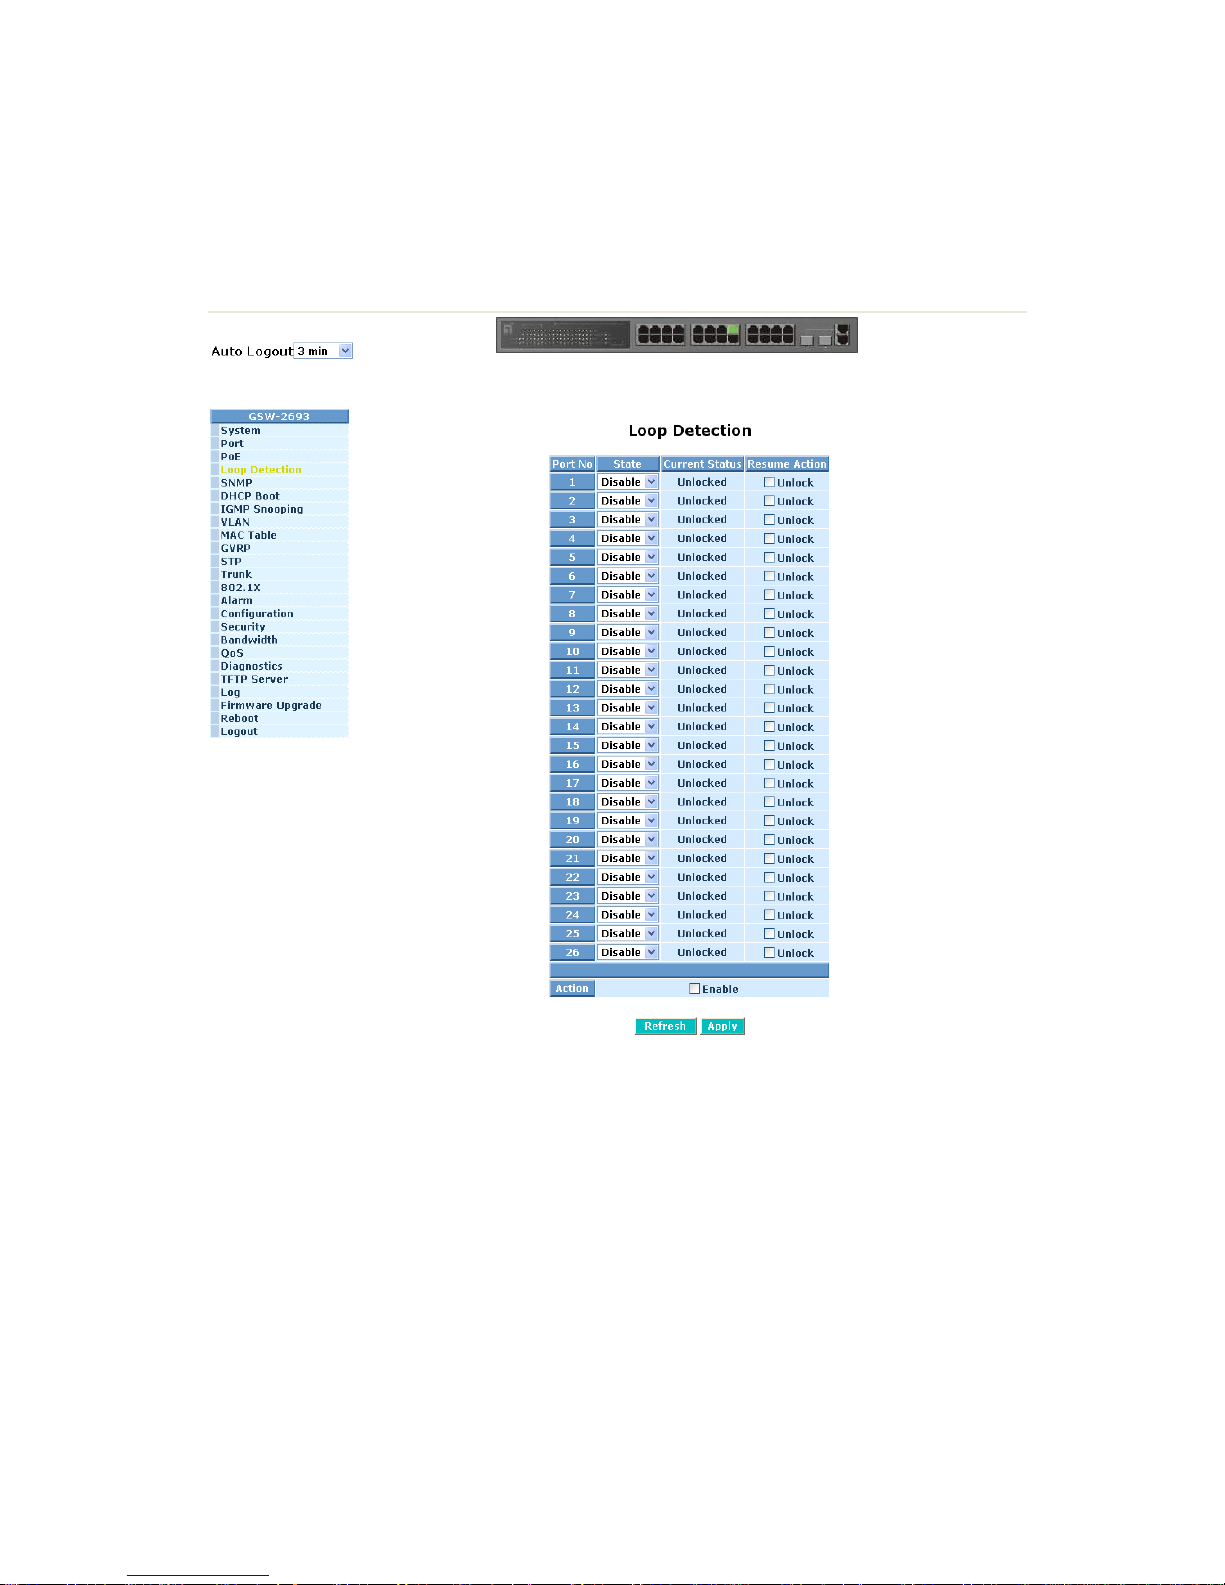
62
3-4. Loop Detection
Looping will always occur when the switches are connected as a cycle and a switch
transmits the packets that will go back to the transmitted switch. Loop Detection will
prevent the looping from happening. Moreover, it could remove the looping
phenomenon per port. In general, you can unplug the cable connection to stop the
looping when a port causes the looping. The switch has powerful Looping Detection
capability, which could cease the looping immediately.
Function name:
Loop Detection
Function description:
This function will start when you enable looping action by ticking the
check box (;) of the Action. That will create some special packet for
looping detection. After enabling looping action, you should decide which
port you would like to open loop detection capability. For example, you
open the loop detection of port 1 as enable state. When the looping
situation happens from port 1, Loop Detection will lock the port1’s ability.
And then you will see that the “Current S tatus” of port 1 shows Locked. In
port status function, you can see that the State of Port Configuration of
port 1 is “Disabled”. So the port 1 will lose the essential ability the port
could have. However , “Resume Action” in Loop Detection will remove the
looping status. It is very convenient for looping happening in real
Page 71
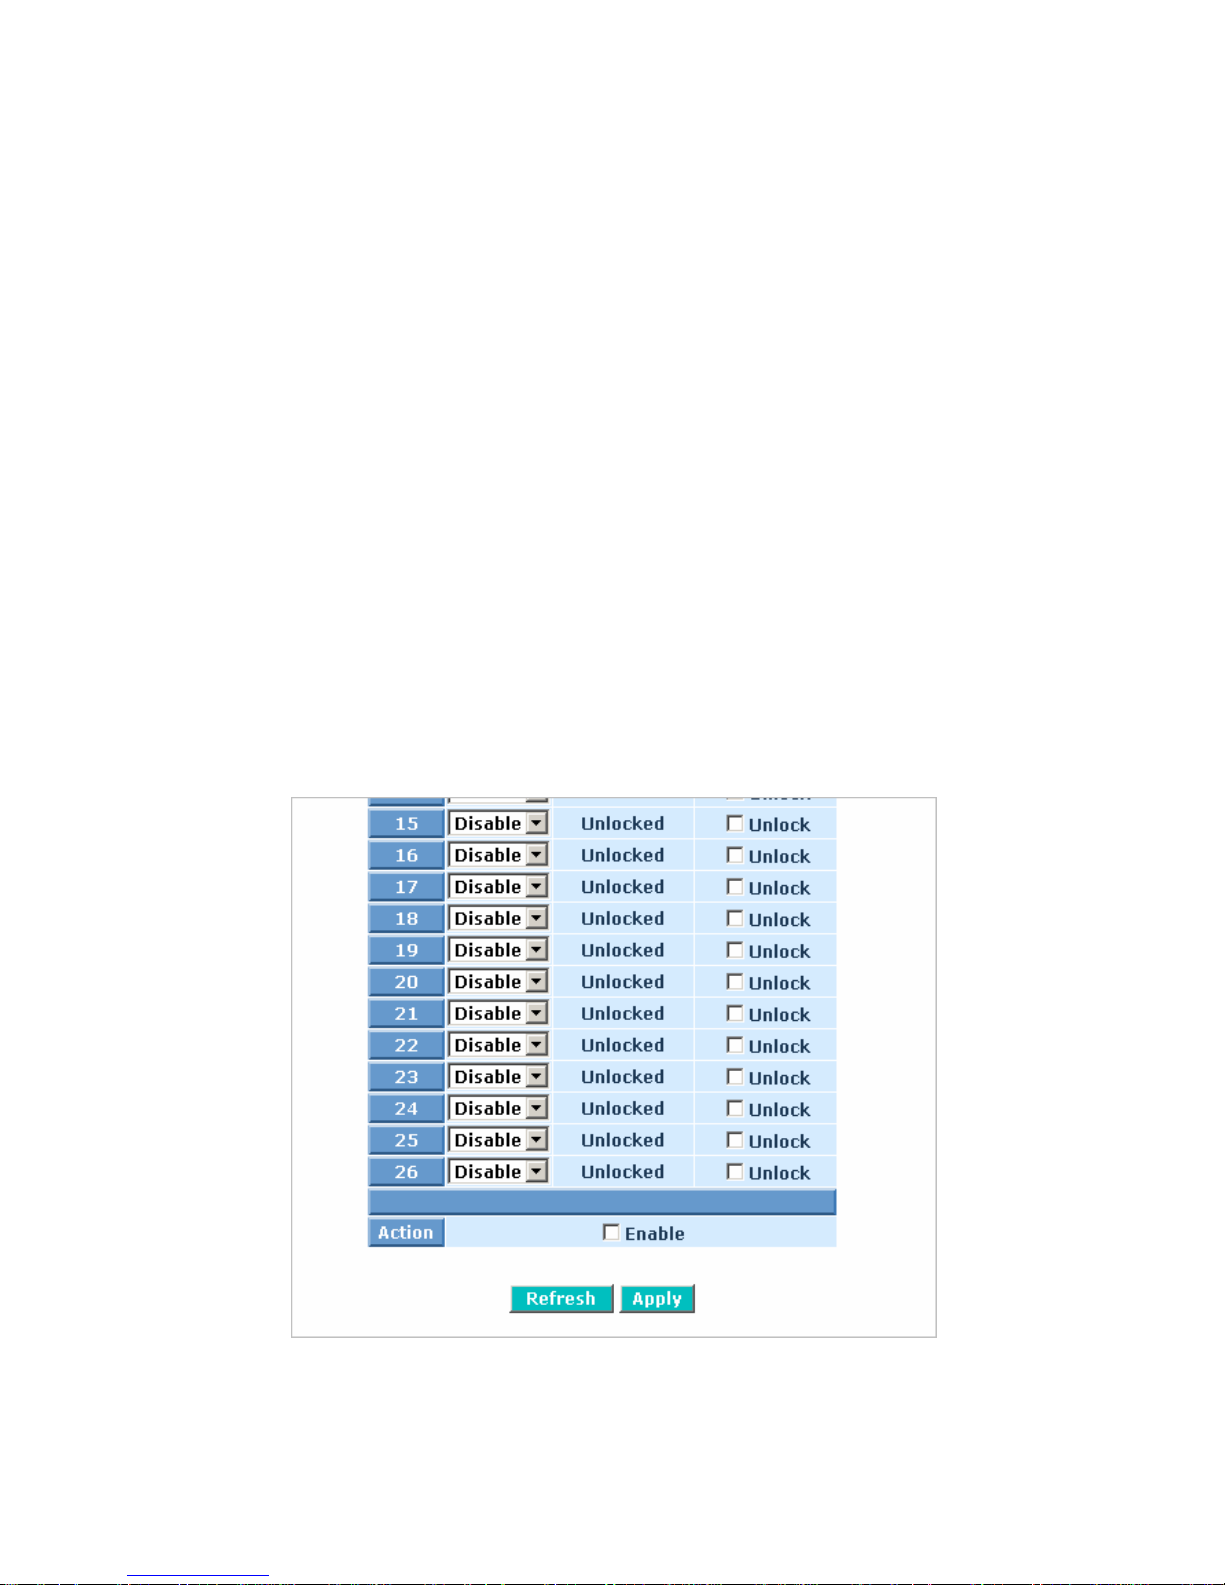
63
networking environment. After any setting you done, please click the
<Apply> button to have the setting taken effect. When looping has
already happened, we suggest that the users could choose the looping
port as “Enable” in advance. And then tick the check box (;) of the
Action. That will get the better result for Looping removing.
Parameters description:
State:
Open the Loop Detection capability per port. The list has “Enable” and
“Disable”. Default is “Disable”.
Current Status:
Show the looping status per port. It could be “Unlocked or Locked”.
Default is “Unlocked”. When some port happens looping, it will show
“Locked”
Resume Action:
Remove the looping status per port. Just tick the check box (;) of the
Unlock to open resume action per port.
Refresh:
“Refresh” button could appear the instant Current Status of Loop
Detection.
Page 72
64
3-5. SNMP Configuration
Any Network Management System (NMS) running the Simple Network
Management Protocol (SNMP) can manage the Managed devices equipped with
SNMP agent, provided that the Management Information Base (MIB) is installed
correctly on the managed devices. The SNMP is a protocol that is used to govern
the transfer of information between SNMP manager and agent and traverses the
Object Identity (OID) of the management Information Base (MIB), described in the
form of SMI syntax. SNMP agent is running on the switch to response the request
issued by SNMP manager.
Basically, it is passive except issuing the trap information. The switch
supports a switch to turn on or off the SNMP agent. If you set the field SNMP
“Enable”, SNMP agent will be started up. All supported MIB OIDs, including RMON
MIB, can be accessed via SNMP manager. If the field SNMP is set “Disable”, SNMP
agent will be de-activated, the related Community Name, Trap Host IP Address,
Trap and all MIB counters will be ignored.
Function name:
SNMP Configuration
Function description:
This function is used to configure SNMP settings, community name, trap host
and public traps as well as the throttle of SNMP. A SNMP manager must pass the
authentication by identifying both community names, then it can access the MIB
information of the target device. So, both parties must have the same community
name. Once completing the setting, click <Apply> button, the setting takes effect.
Parameters description:
SNMP:
The term SNMP here is used for the activation or de-activation of SNMP.
Default is Enable.
Get/Set/Trap Community:
Community name is used as password for authenticating if the
requesting network management unit belongs to the same community
group. If they both don’t have the same community name, they don’t
belong to the same group. Hence, the requesting network management
unit can not access the device with different community name via SNMP
protocol; If they both have the same community name, they can talk each
other.
Community name is user-definable with a maximum length of 15
characters and is case sensitive. There is not allowed to put any blank in
the community name string. Any printable character is allowable.
The community name for each function works independently. Each
function has its own community name. Say, the community name for
GET only works for GET function and can’t be applied to other function
such as SET and Trap.
Page 73
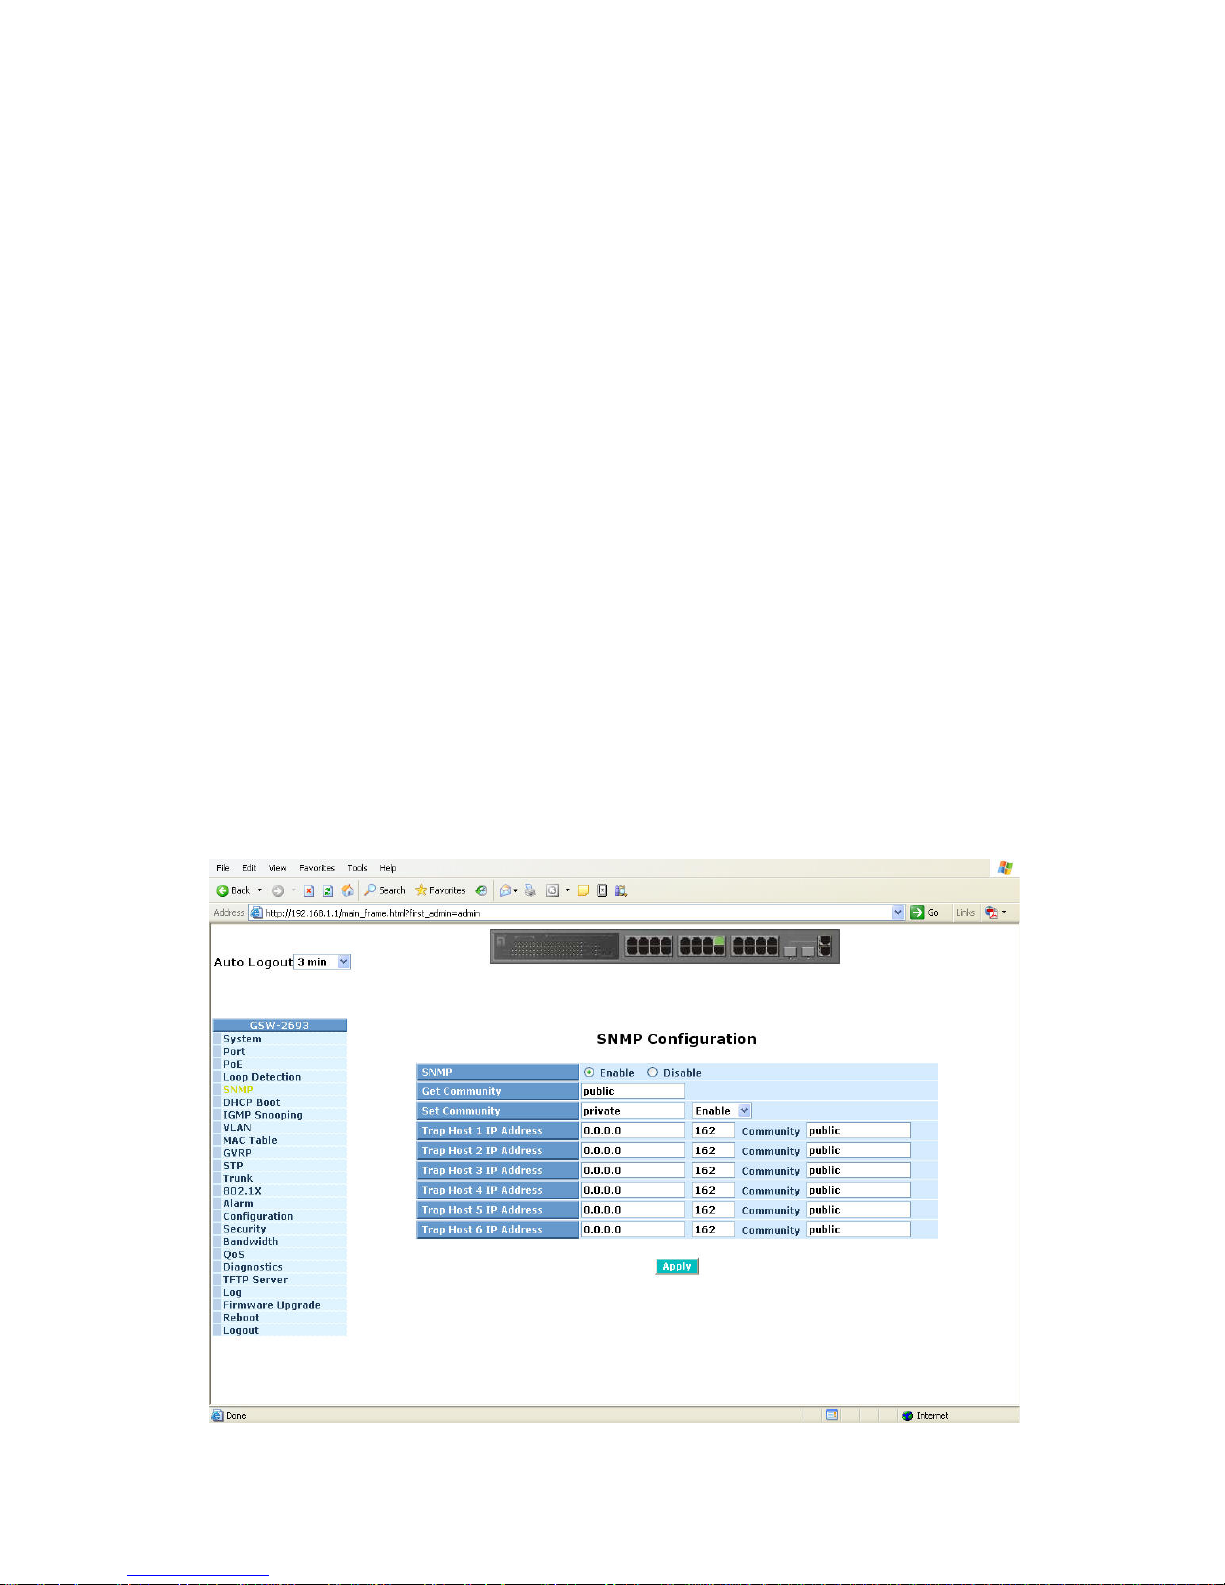
65
Default SNMP function : Enable
Default community name for GET: public
Default community name for SET: private
Default community name for Trap: public
Default Set function : Enable
Default trap host IP address: 0.0.0.0
Default port number :162
Trap:
In the switch, there are 6 trap hosts supported. Each of them has its own
community name and IP address; is user-definable. To set up a trap host
means to create a trap manager by assigning an IP address to host the
trap message. In other words, the trap host is a network management
unit with SNMP manager receiving the trap message from the managed
switch with SNMP agent issuing the trap message. 6 trap hosts can
prevent the important trap message from losing.
For each public trap, the switch supports the trap event Cold Start, Warm
Start, Link Down, Link Up and Authentication Failure Trap. They can be
enabled or disabled individually. When enabled, the corresponded trap
will actively send a trap message to the trap host when a trap happens. If
all public traps are disabled, no public trap message will be sent. As to
the Enterprise (no. 6) trap is classified as private trap, which are listed in
the Trap Alarm Configuration function folder.
Default for all public traps: Enable.
Fig. 3-17 Community and trap host setting
Page 74
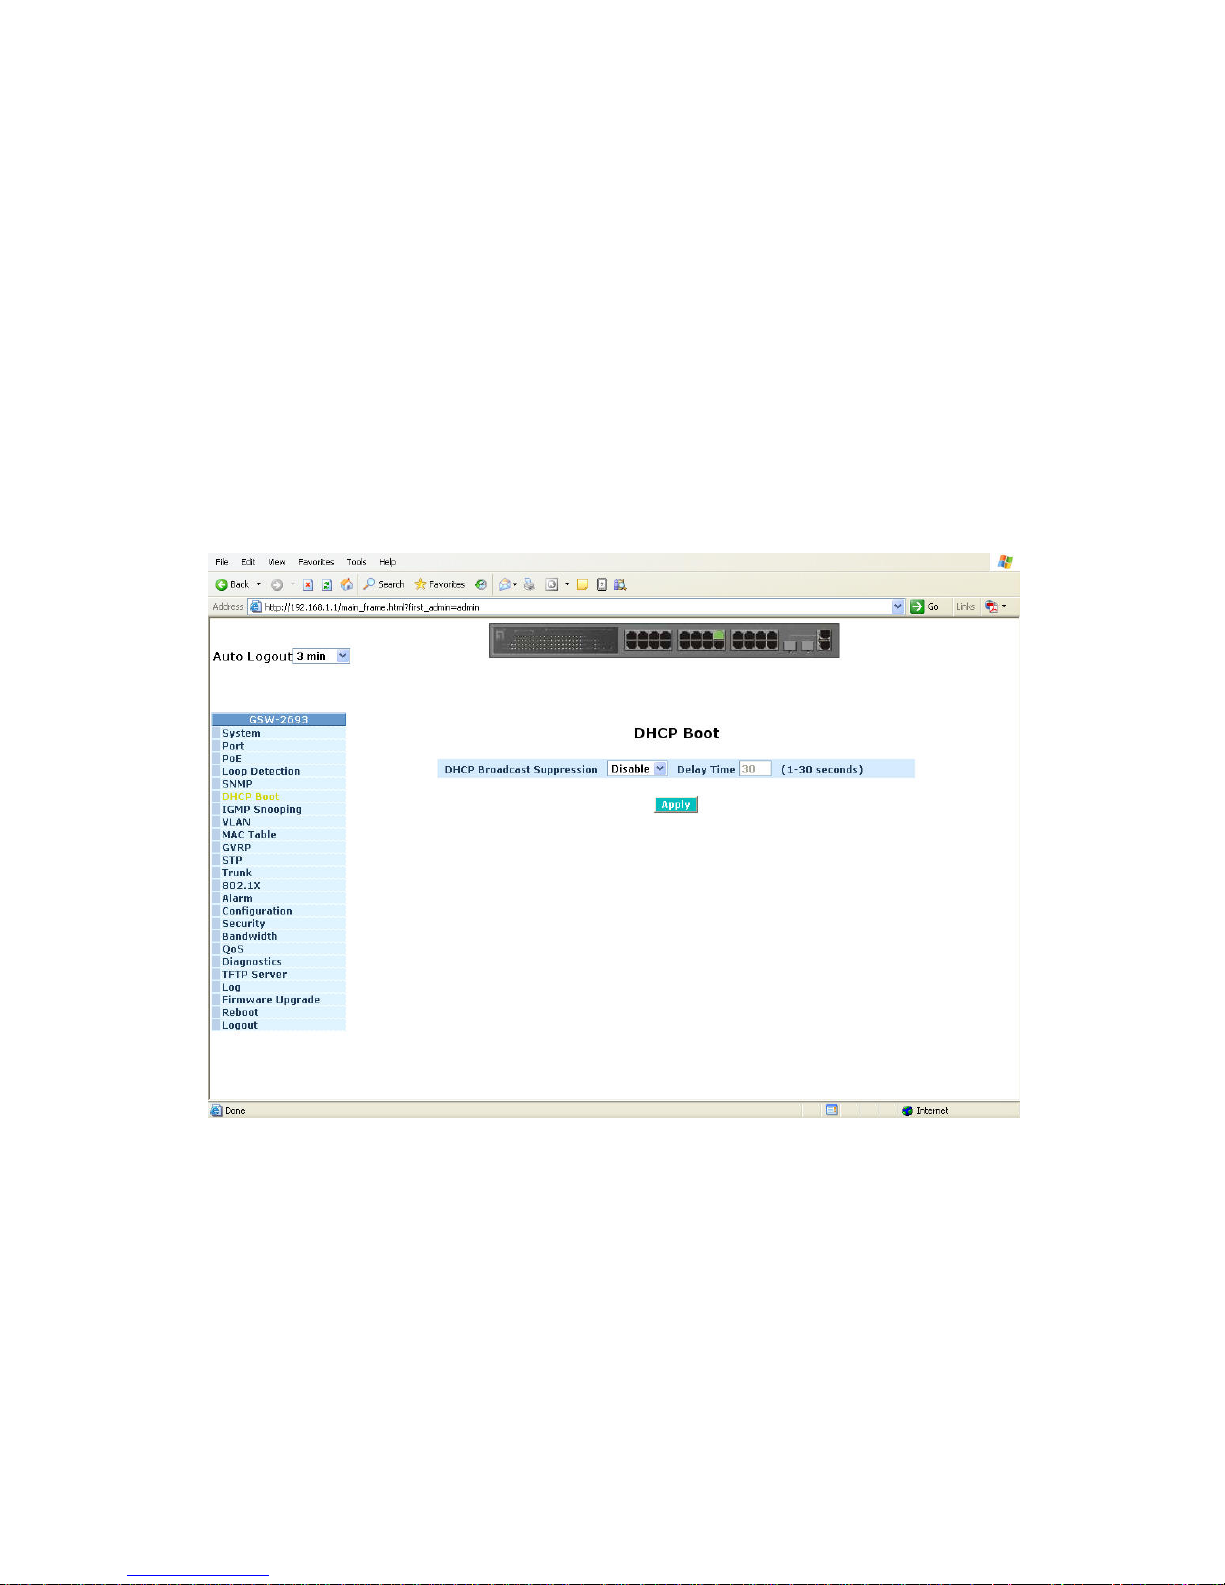
66
3-6. DHCP Boot
The DHCP Boot function is used to spread the request broadcast packet into
a bigger time frame to prevent the traffic congestion due to broadcast packets from
many network devices which may seek its NMS, boot server, DHCP server and
many connections predefined when the whole building or block lose the power and
then reboot and recover. At this moment, a bunch of switch or other network device
on the LAN will try its best to find the server to get the services or try to set up the
predefined links, they will issue many broadcast packets in the network.
The switch supports a random delay time for DHCP and boot delay for each
device. This suppresses the broadcast storm while all devices are at booting stage
in the same time. The maximum user-defined delay time is 30 sec. If DHCP
Broadcasting Suppression function is enabled, the delay time is set randomly,
ranging from 0 to 30 seconds, because the exactly delay time is computed by the
switch itself. The default is “Disable”.
Fig. 3-18
Page 75
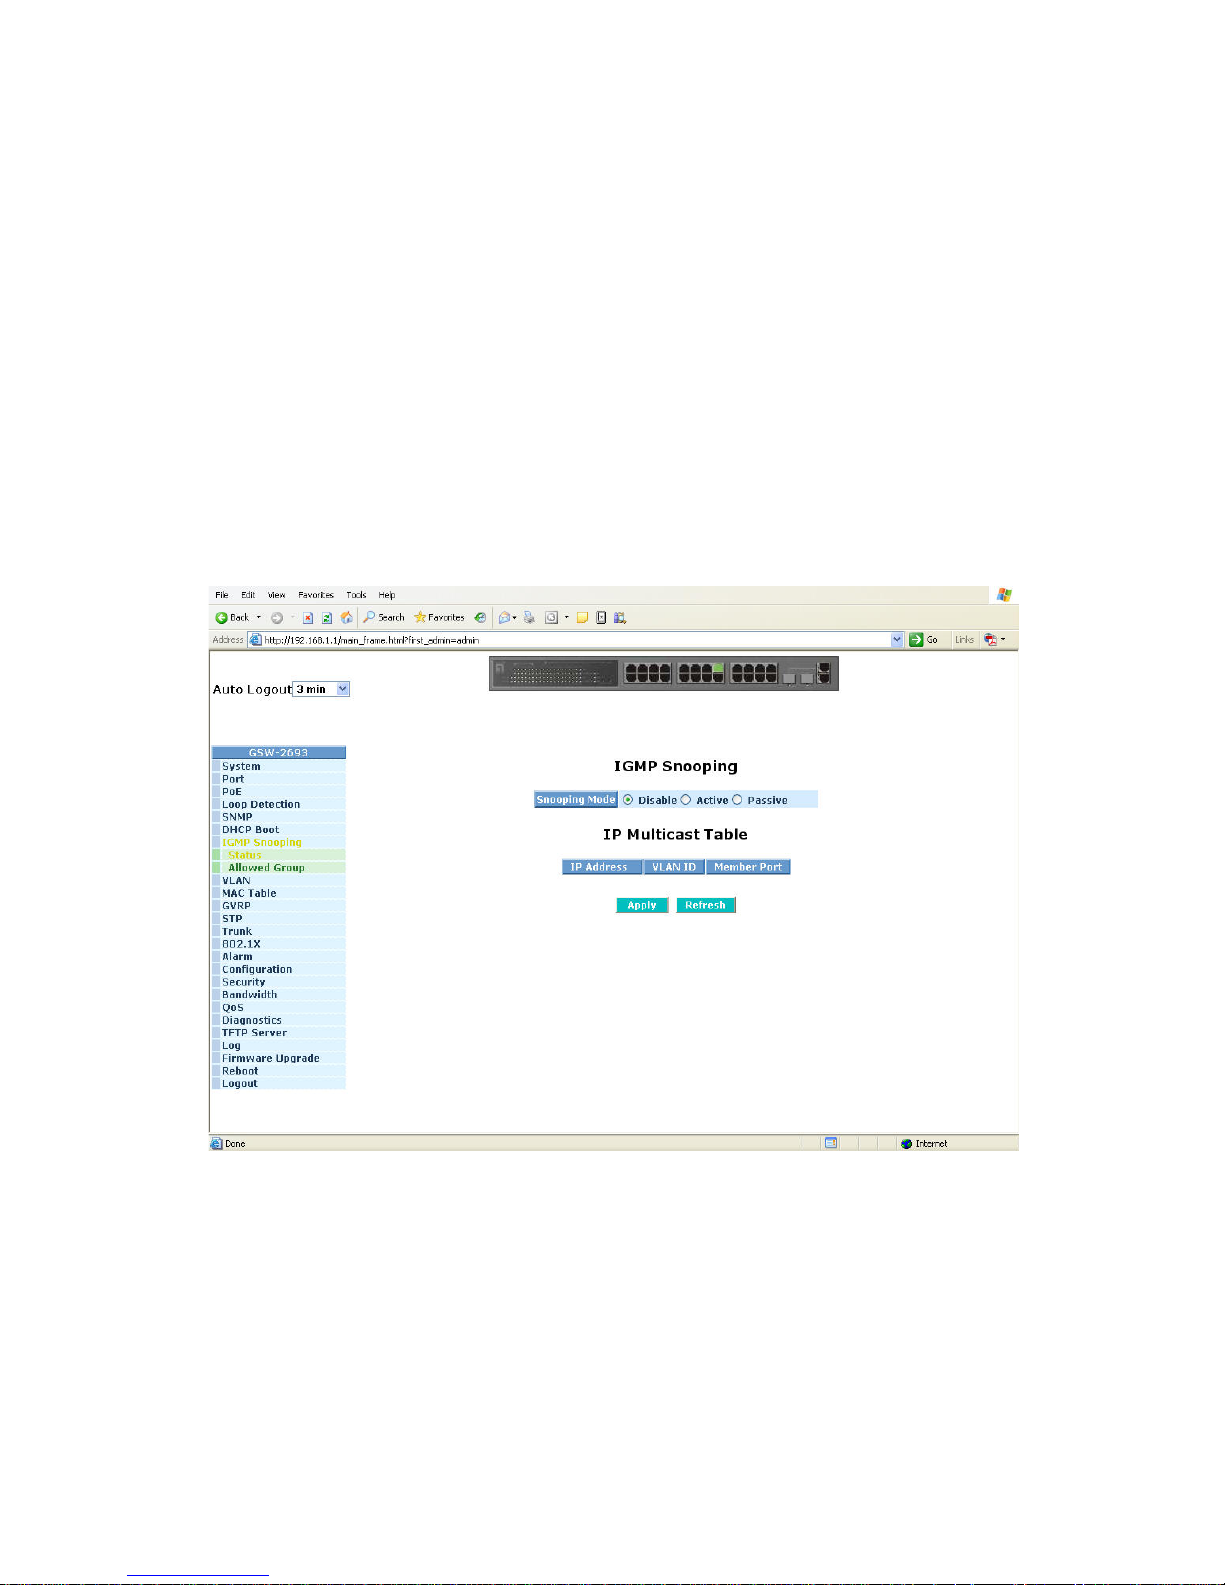
67
3-7. IGMP Snooping
The function, IGMP Snooping, is used to establish the multicast groups to
forward the multicast packet to the member ports, and, in nature, avoids wasting the
bandwidth while IP multicast packets are running over the network. This is because
a switch that does not support IGMP or IGMP Snooping can not tell the multicast
packet from the broadcast packet, so it can only treat them all as the broadcast
packet. Without IGMP Snooping, the multicast packet forwarding function is plain
and nothing is different from broadcast packet.
A switch supported IGMP Snooping with the functions of query, report and
leave, a type of packet exchanged between IP Multicast Router/Switch and IP
Multicast Host, can update the information of the Multicast table when a member
(port) joins or leaves an IP Multicast Destination Address. With this function, once a
switch receives an IP multicast packet, it will forward the packet to the members
who joined in a specified IP multicast group before.
The packets will be discarded by the IGMP Snooping if the user transmits
multicast packets to the multicast group that had not been built up in advance.
Fig. 3-19
Function name:
IGMP Snooping Status
Function description:
IGMP is used to snoop the status of IP multicast groups and display its
associated information in both tagged VLAN and non-tagged VLAN networks.
Enabling IGMP with either passive or active mode, you can monitor the IGMP
snooping information, which contains the multicast member list with the
multicast groups, VID and member port.
Page 76
68
Parameter description:
IGMP snooping mode selection:
The switch supports three kinds of IGMP Snooping status, including
“Passive”, “Active” and “Disable”.
Disable:
Set “Disable” mode to disable IGMP Snooping function.
Default: Disable
Active:
In Active mode, IGMP snooping switch will periodically issue the
Membership Query message to all hosts attached to it and
gather the Membership report message to update the database
of the Multicast table. By the way, this also reduces the
unnecessary multicast traffic.
Passive:
In Passive Snooping mode, the IGMP snooping will not
periodically poll the hosts in the groups. The switch will send a
Membership Query message to all hosts only when it has
received a Membership Query message from a router.
IP Address:
Show all multicast groups IP addresses that are registered on this device.
VLAN ID:
Show VLAN ID for each multicast group.
Member Port:
Show member ports that join each multicast group. Member port may be
only or more than one.
Page 77
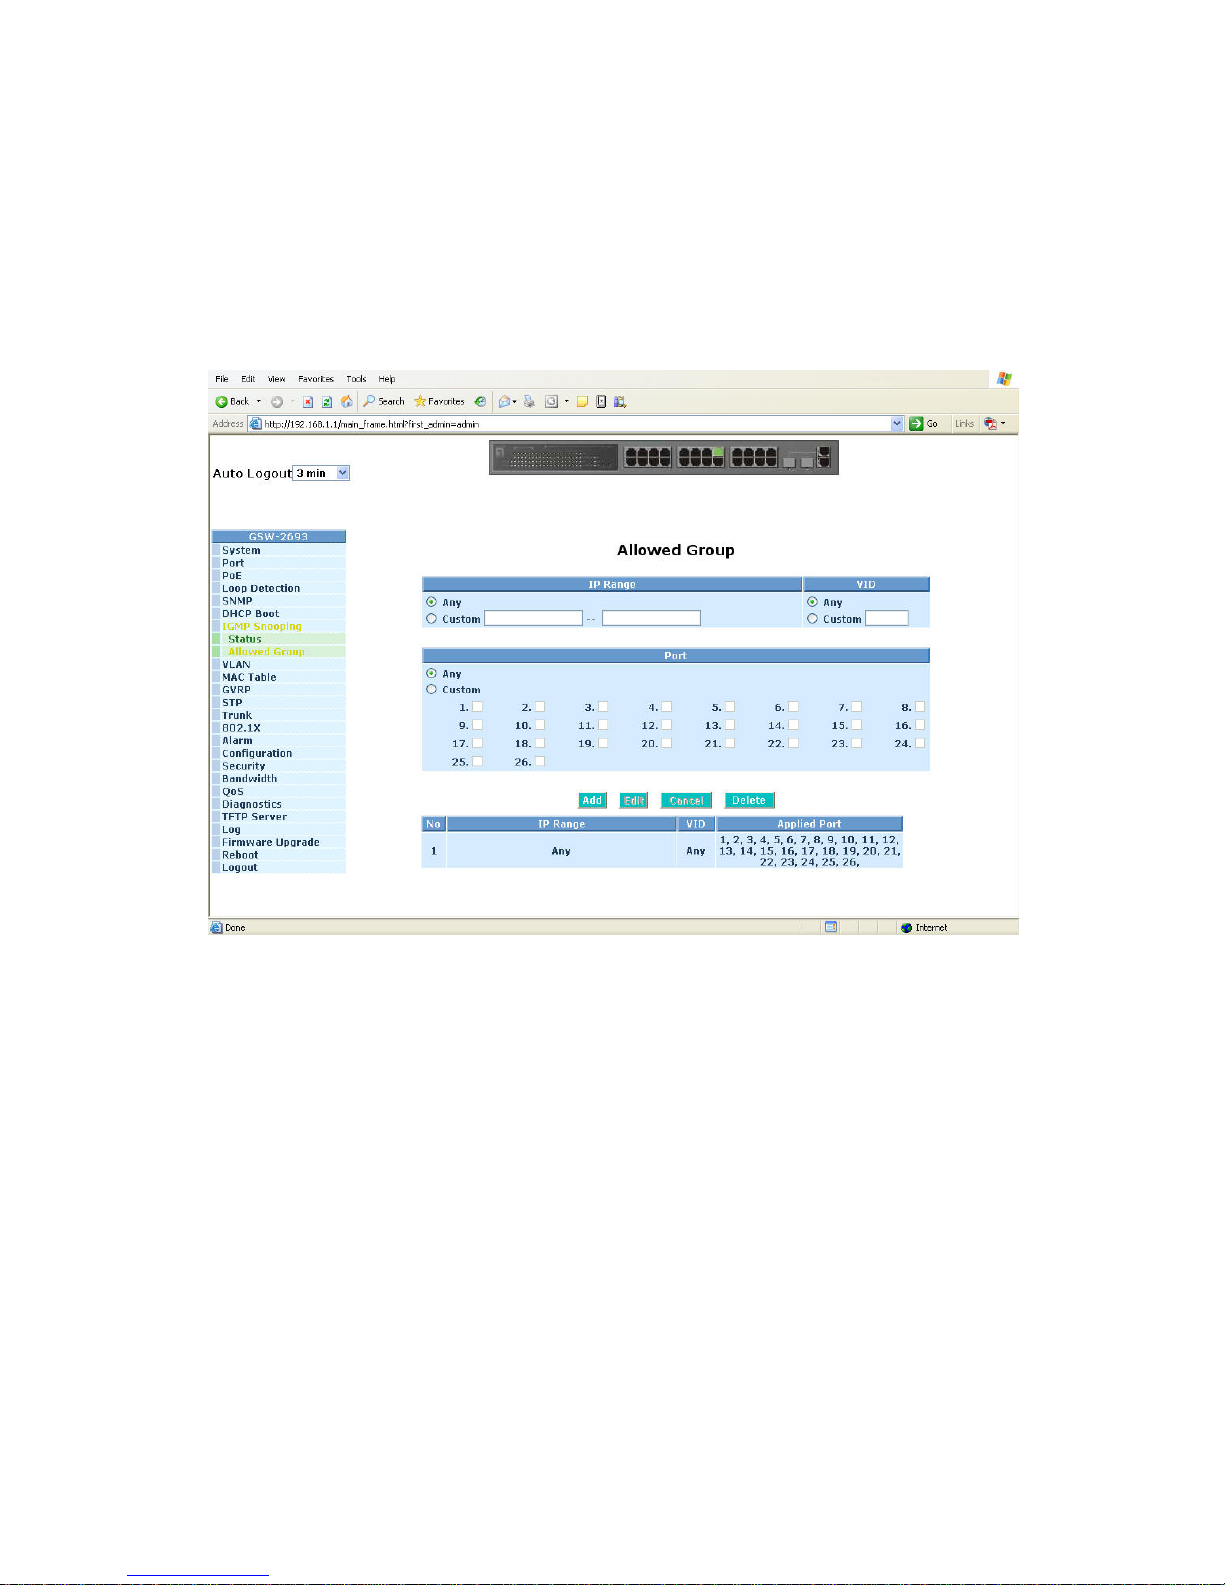
69
Function name:
Allowed Group
Function description:
The Allowed Group function allows the IGMP Snooping to set up the IP
multicast table based on user’s specific conditions. IGMP report packets that
meet the items you set up will be joined or formed the multicast group.
Fig. 3-20
Parameter description:
IP Range:
The switch supports two kinds of options for managed valid IP range,
including “Any” and “Custom”. Default is “Any”. In case that” Custom”
had been chosen, you can assigned effective IP range. The valid range
is 224.0.0.0~239.255.255.255.
VID:
The switch supports two kinds of options for managed valid VLAN VID,
including “Any” and “Custom”. Default is “Any”. When you choose
“Custom”, you can fill in VID number. The valid VID range is 1~4094.
Port:
The switch supports two kinds of options for managed valid port range,
including “Any” and “Custom”. Default is “Any”. You can select the ports
that you would like them to be worked and restricted in the allowed group
configuration if ”Custom” had been chosen.
Page 78
70
Add:
A new entry of
allowed group configuration can be created after the
parameters as mentioned above had been setup and then press <Add>
button.
Edit:
The existed entry also can be modified after pressing <Edit> button.
Delete:
Remove the existed entry of allowed group configuration from the
allowed group.
Page 79
71
3-8. VLAN
The switch supports Tag-based VLAN (802.1q) and Port-based VLAN.
Support 256 active VLANs and VLAN ID 1~4094. VLAN configuration is used to
partition your LAN into small ones as your demand. Properly configuring it, you can
gain not only improving security and increasing performance but greatly reducing
VLAN management.
3-8-1. VLAN Mode
Function name:
VLAN Mode Setting
Function description:
The VLAN Mode Selection function includes two modes: Port-based and Tagbased, you can choose one of them by pulling down list and pressing the
<Downward> arrow key. Then, click <Apply> button, the settings will take
effect immediately.
Parameter description:
VLAN Mode:
Tag-based:
This is the default setting.
Tag-based VLAN identifies its member by VID. This is quite
different from port-based VLAN. If there are any more rules in
ingress filtering list or egress filtering list, the packet will be
screened with more filtering criteria to determine if it can be
forwarded. The switch support s supple m ent of 802.1q..
Each tag-based VLAN you built up must be assigned VLAN name
and VLAN ID. Valid VLAN ID is 1-4094. User can create total up to
256 Tag VLAN groups.
Port-based:
Port-based VLAN is defined by port. Any packet coming in or
outgoing from any one port of a port-based VLAN will be accepted.
No filtering criterion applies in port-based VLAN. The only criterion
is the physical port you connect to. For example, for a port-based
VLAN named PVLAN-1 contains port members Port 1&2&3&4. If
you are on the port 1, you can communicate with port 2&3&4. If you
are on the port 5, then you cannot talk to them. Each port-based
VLAN you built up must be assigned a group name. This switch can
support up to maximal 26 port-based VLAN groups.
Metro Mode:
The Metro Mode is a quick configuration VLAN environment
method on Port-based VLAN. It will create 22 or 23 Port-based
VLAN groups.
Page 80
72
Symmetric Vlan:
This is a Ingress Rule (Rule 1, The Ingress Filtering Rule 1 is “forward
only packets with VID matching this port’s configured VID”.). For example,
if port 1 receives a tagged packet with VID=100 (VLAN name=VLAN100),
and if Symmetric-Vlan function is enabled, the switch will check if port 1
is a member of VLAN100. If yes, the received packet is forwarded;
otherwise, the received packet is dropped.
Note: If Symmetric is enabled and port 1, for example, receives an untagged packet,
the switch will apply the PVID of port 1 to tag this packet, the packet then will
be forwarded. But if the PVID of port 1 is not 100, the packet will be dropped.
SVL:
While SVL is enable, all VLANs use the same filtering database storing
the membership information of the VLAN to learn or look up the
membership information of the VLAN. While SVL is disable, it means
learning mode is IVL. In this mode, different VLAN uses different filtering
database storing the membership information of the VLAN to learn or
look up the information of a VLAN member.
Double Tag:
Double-tag mode belongs to the tag-based mode, however, it would treat
all frames as the untagged ones, which means that tag with PVID will be
added into all packets. Then, these packets will be forwarded as Tagbased VLAN. So, the incoming packets with tag will become the doubletag ones.
Up-link Port:
This function is enabled only when metro mode is chosen in VLAN mode.
25:
Except Port 25, each port of the switch cannot transmit packets with
each other. Each port groups a VLAN with Port 25, thus, total 23
groups consisting of 2 members are formed.
26:
Except Port 26, each port of the switch cannot transmit packets with
each other. Each port groups a VLAN with Port 26, thus, total 23
groups consisting of 2 members are formed.
25&26:
Except Port 25 and Port 26, each port of the switch cannot transmit
packets with each other. Each port groups a VLAN with Port 25
and Port 26, thus, total 22 groups consisting of 3 members are
formed.
Page 81
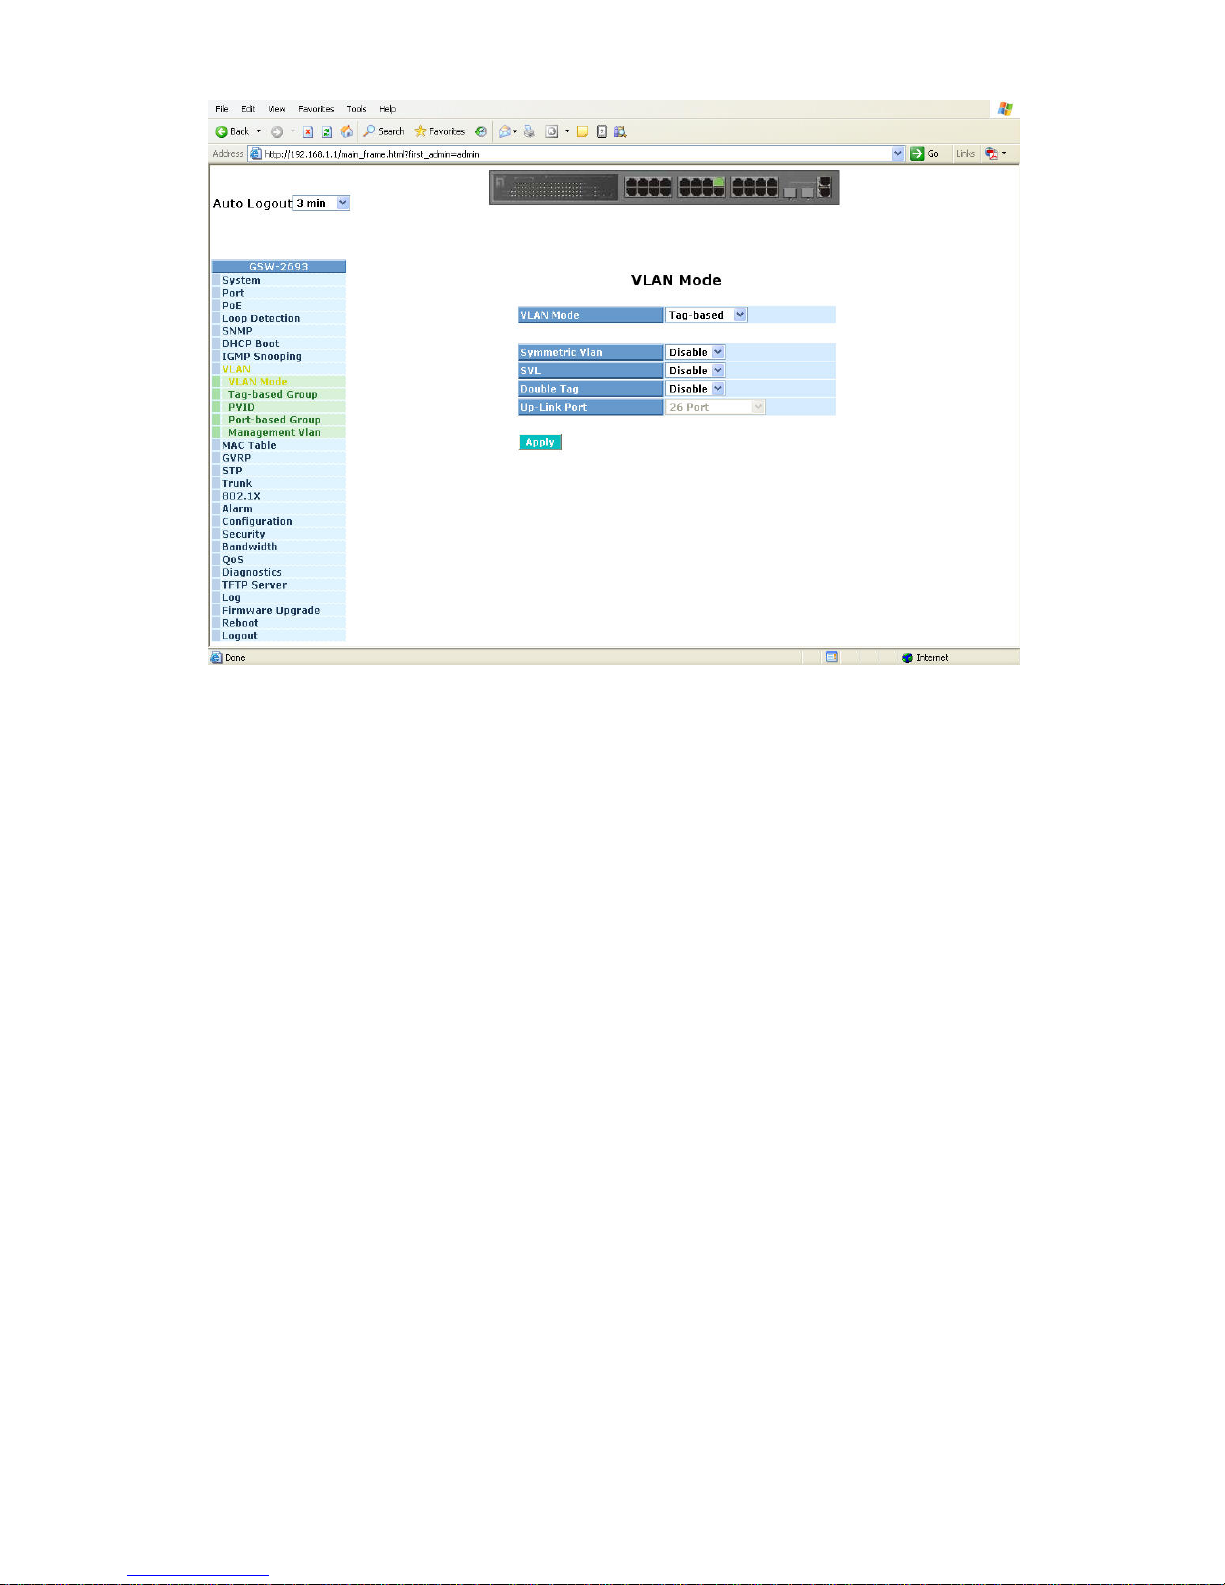
73
Fig. 3-21
Page 82
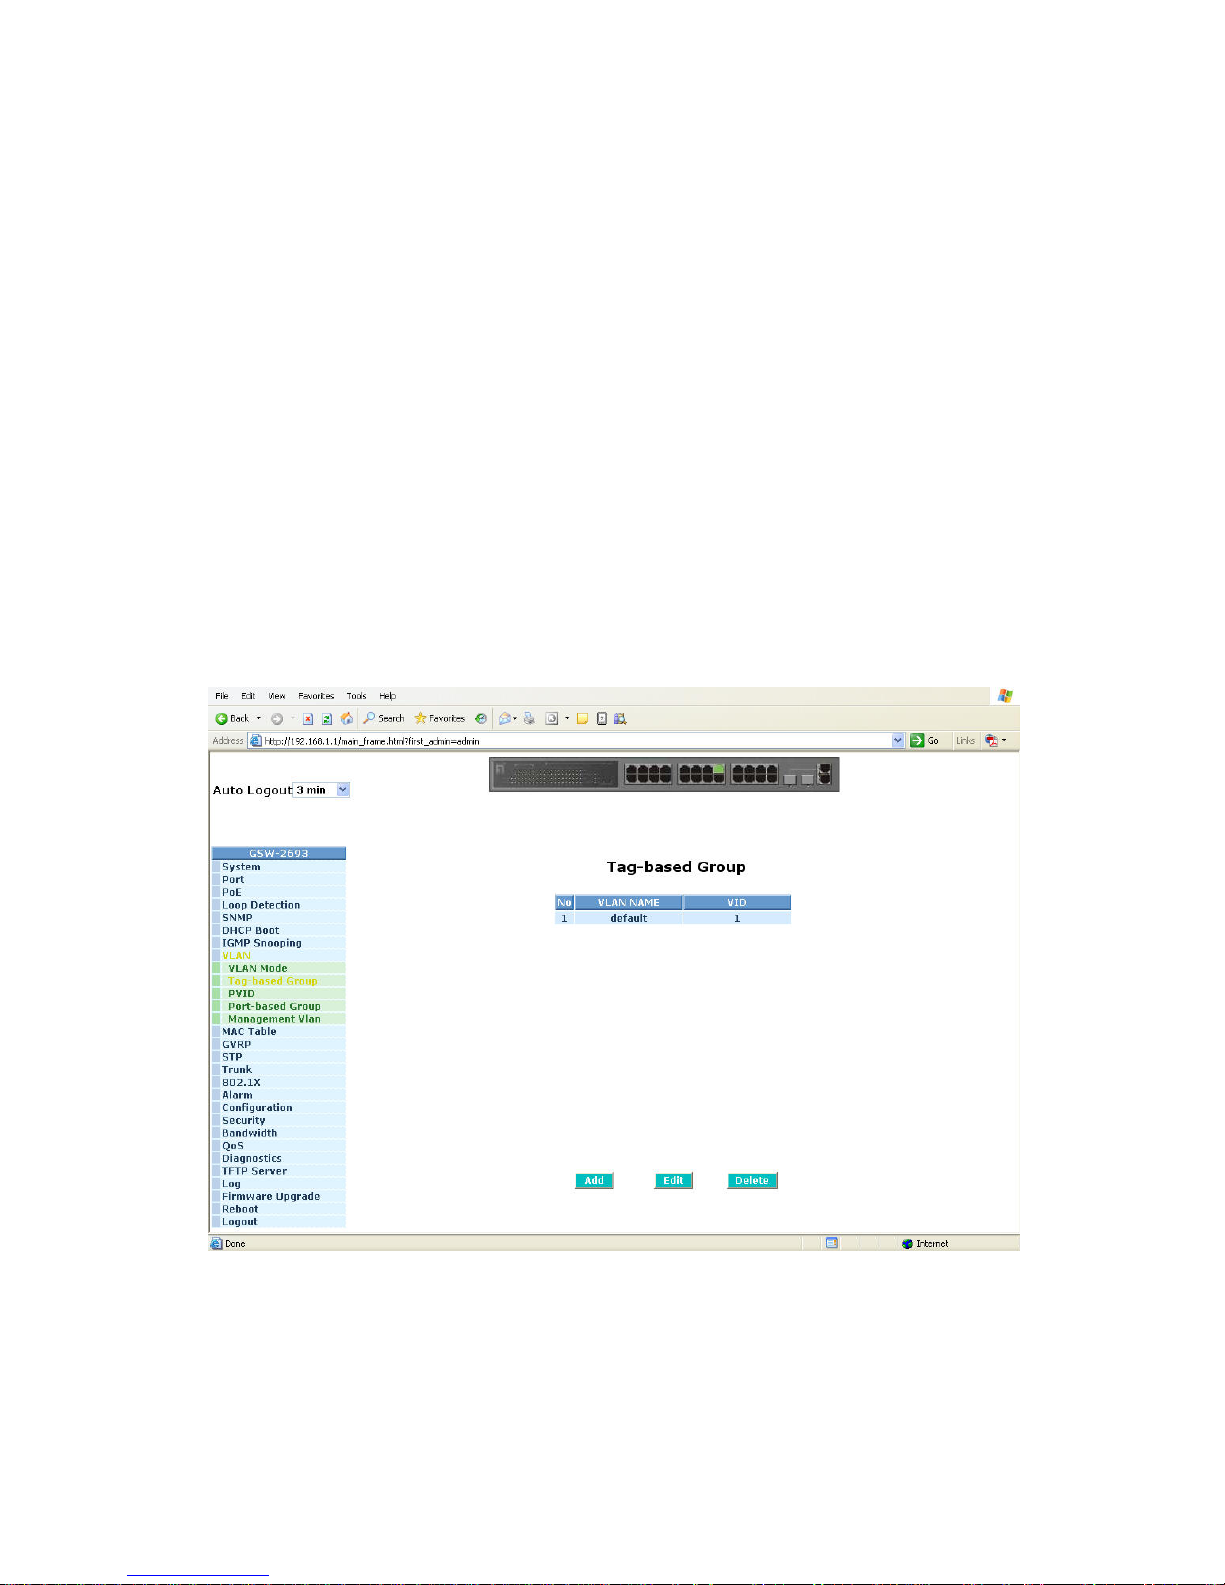
74
3-8-2. Tag-based Group
Function name:
Tag-based Group Configuration
Function description:
It shows the information of existed Tag-based VLAN Groups. You can also
easily create, edit and delete a Tag-based VLAN group by pressing <Add>,
<Edit> and <Delete> function buttons. User can add a new VLAN group by
inputting a new VLAN name and VLAN ID after pressing <Add> button.
Parameter description:
VLAN Name:
The name defined by administrator is associated with a VLAN group.
Valid letters are A-Z, a-z, 0-9, “
- “ and “_” characters. The maximal
length is 15 characters.
VID:
VLAN identifier. Each tag-based VLAN group has a unique VID. It
appears only in tag-based and Double-tag mode.
Fig. 3-22
Page 83
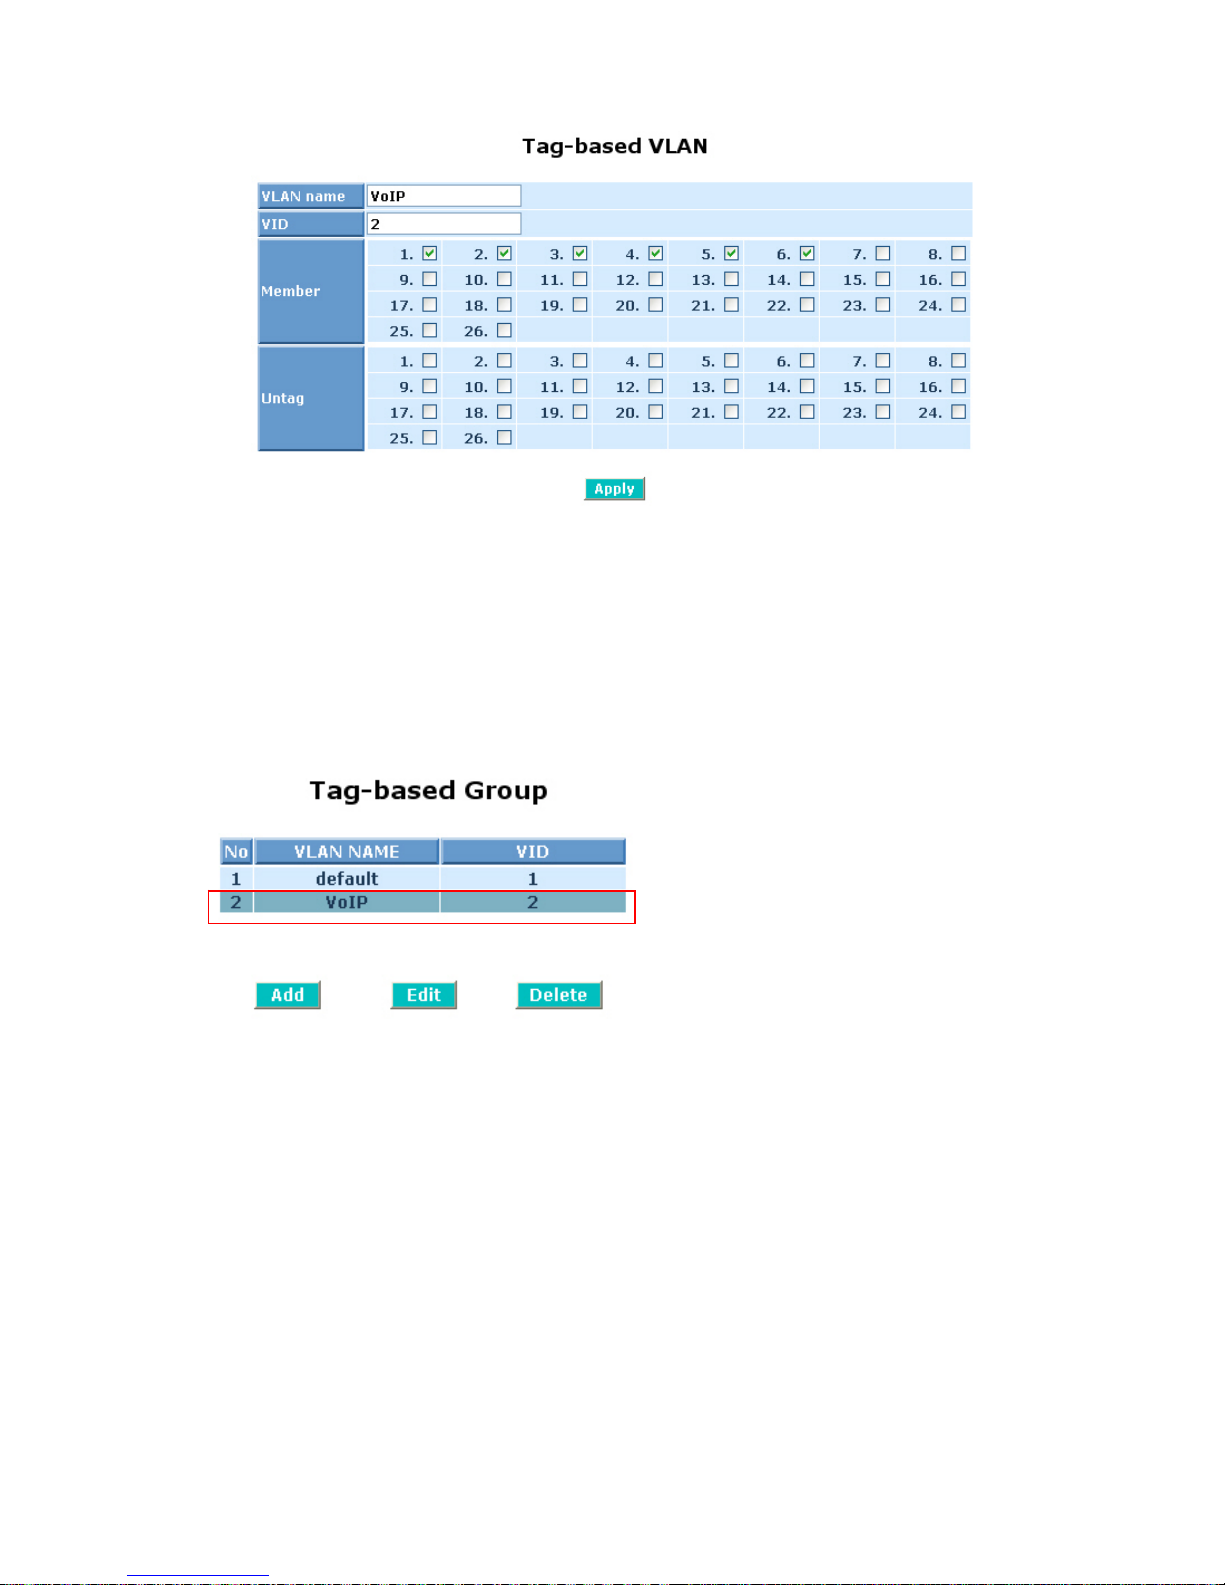
75
Add Group:
Input the VLAN name, VID and then choose the member by ticking the
check box beside the port No. to create a new Tag-based VLAN. As to
the parameter of Untag, it stands for an egress rule of the port. If you tick
the check box beside the port No., packets with this VID outgoing from
this port will be untagged. Finally, press the <Apply> button to have the
setting taken effect.
After Tag-based Group created, user can Edit or Delete specified group by
selecting group name
Delete Group:
Just press the <Delete> button to remove the selected group ent ry from
the Tag-based group table.
Edit a group:
Just select a group entry and press the <Edit> button, then you can
modify a group’s description, member and untag settings.
Page 84
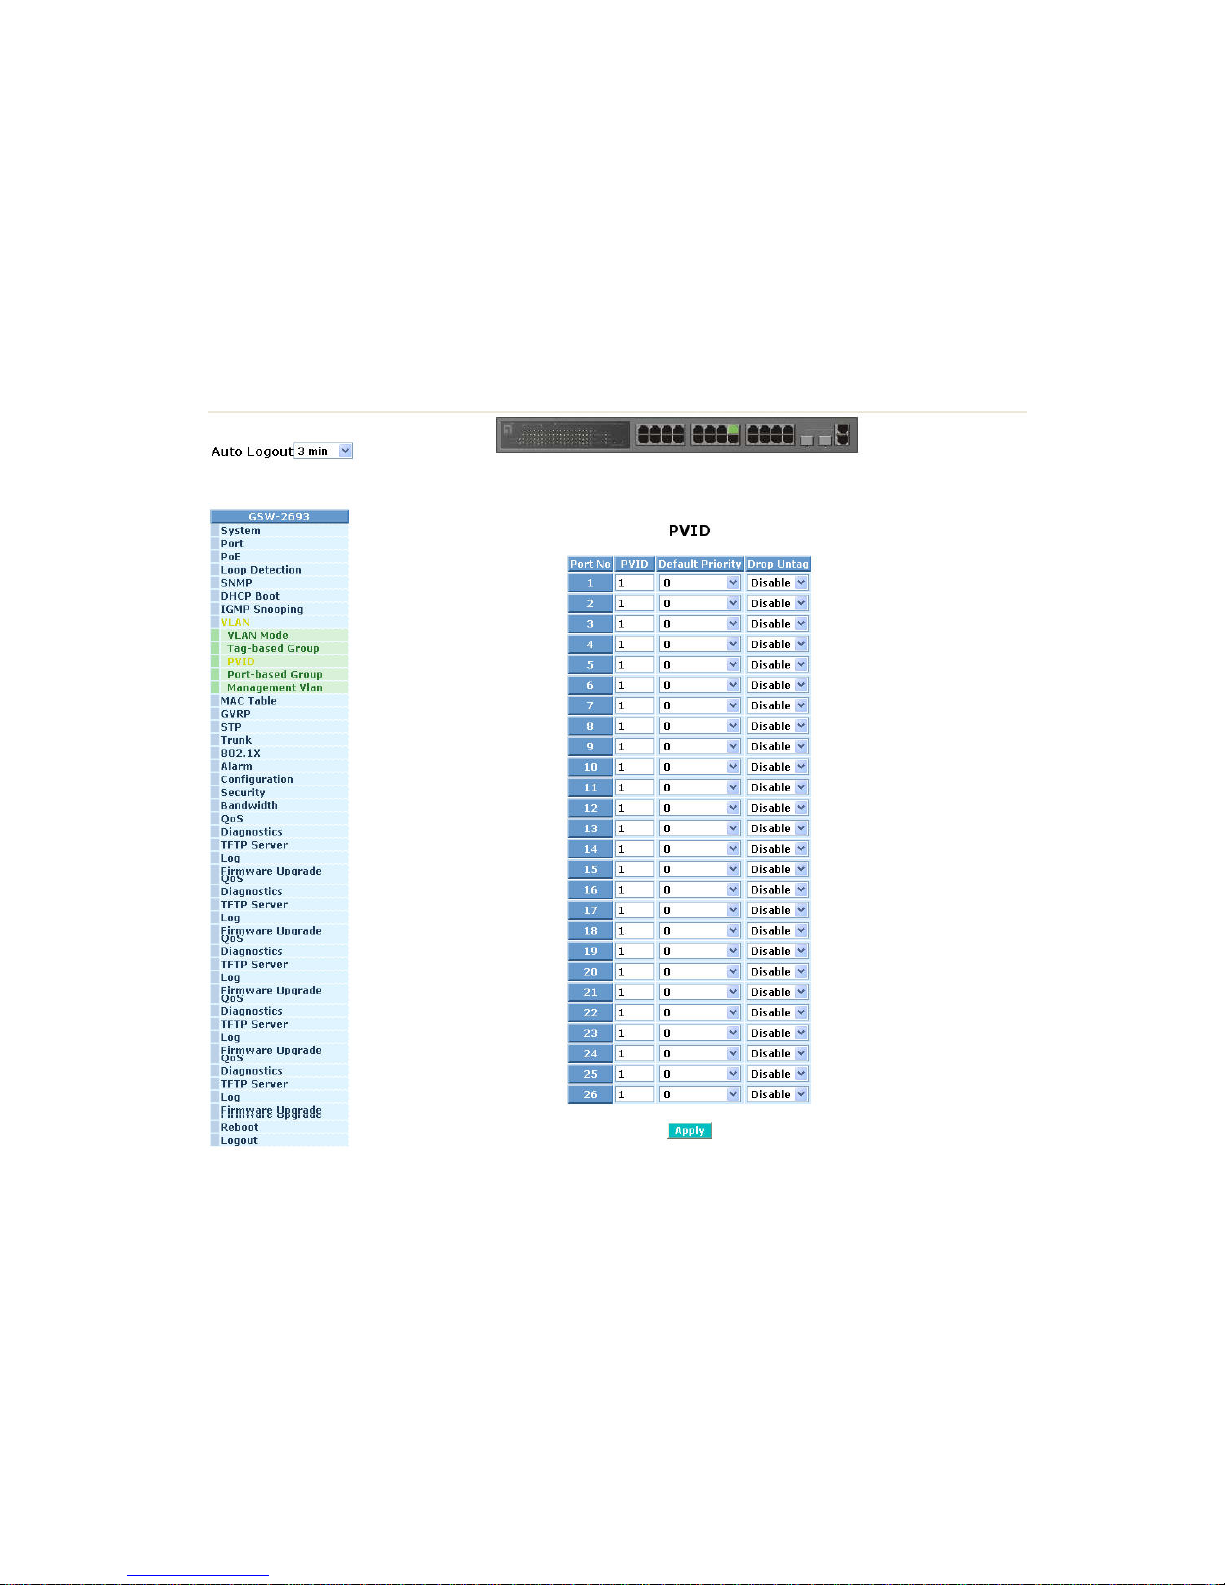
76
3-8-3. PVID
Function name:
PVID
Function description:
In PVID Setting, user can input VID number to each port. The range of VID
number is from 1 to 4094. User also can choose ingress filtering rule (Rule 2)
to each port. The Ingress Filtering Rule 2 is “drop untagged frame”. While Rule
2 is enabled, the port will discard all Untagged-frames.
Fig. 3-25
Parameter description:
Port 1-26:
Port number.
PVID:
This PVID range will be 1-4094. Before you set a number x as PVID, you
have to create a Tag-based VLAN with VID x. For example, if port x
receives an untagged packet, the switch will apply the PVID (assume as
VID y) of port x to tag this packet, the packet then will be forwarded as
the tagged packet with VID y.
Page 85
77
Default Priority:
It bases on 802.1p QoS and affects untagged packets. When the packets
enter the switch, it would get the priority precedence according to your
Default Priority setting and map to 802.1p priority setting in QoS function.
For example, while you set Default Priority of port 2 with 2 and transmit
untagged packets to port 2, these packets will own priority 2 precedence
due to your default 802.1p Priority Mapping setting in QoS function and
be put into Queue 1.
Drop Untag:
Drop untagged frame. You can configure a given port to accept all frames
(Tagged and Untagged) or just receive tagged frame. If the former is the
case, then the packets with tagged or untagged will be processed. If the
later is the case, only the packets carrying VLAN tag will be processed,
the rest packets will be discarded.
Page 86
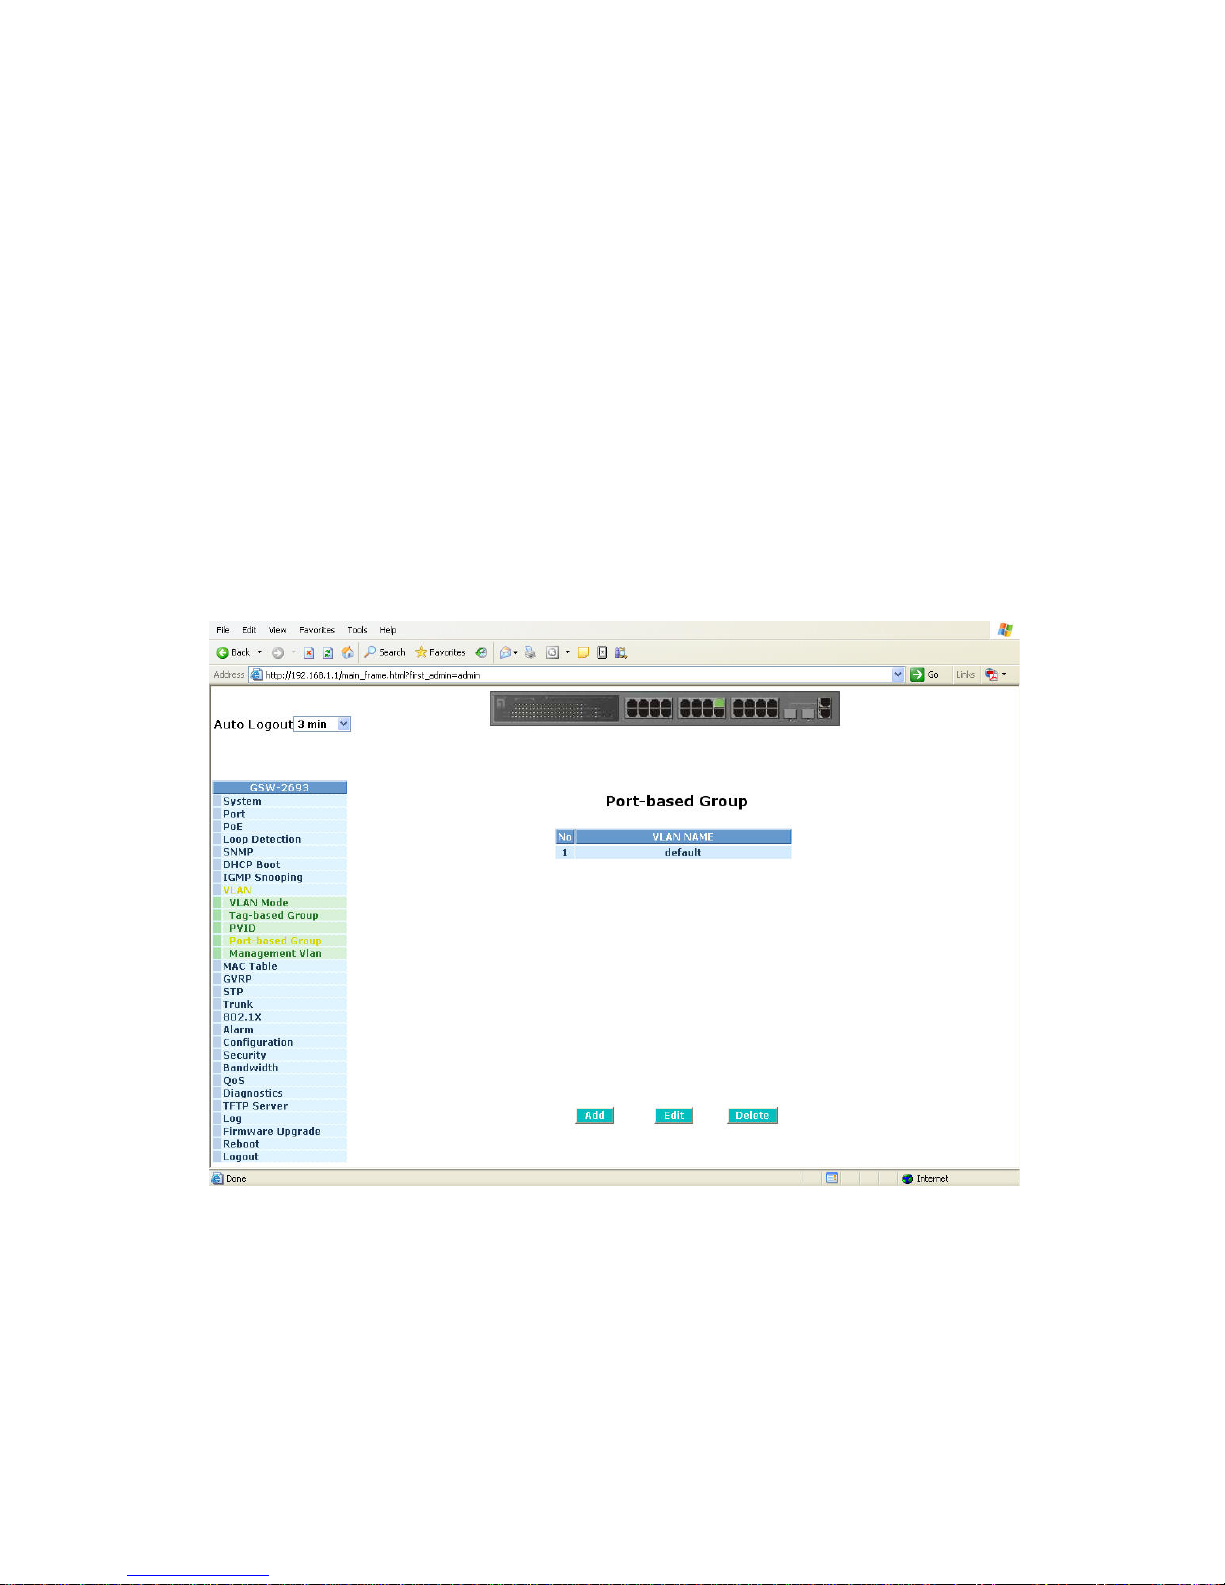
78
3-8-4. Port-based Group
Function name:
Port-based Group Configuration
Function description:
It shows the information of the existed Port-based VLAN Groups. You can
easily create, edit and delete a Port-based VLAN group by pressing <Add>,
<Edit> and <Delete> function buttons. User can add a new VLAN group by
inputting a new VLAN name.
Parameter description:
VLAN Name:
The name defined by administrator is associated with a VLAN group.
Valid letters are A-Z, a-z, 0-9, “
- “ and “_” characters. The maximal
length is 15 characters.
Fig. 3-26
Page 87
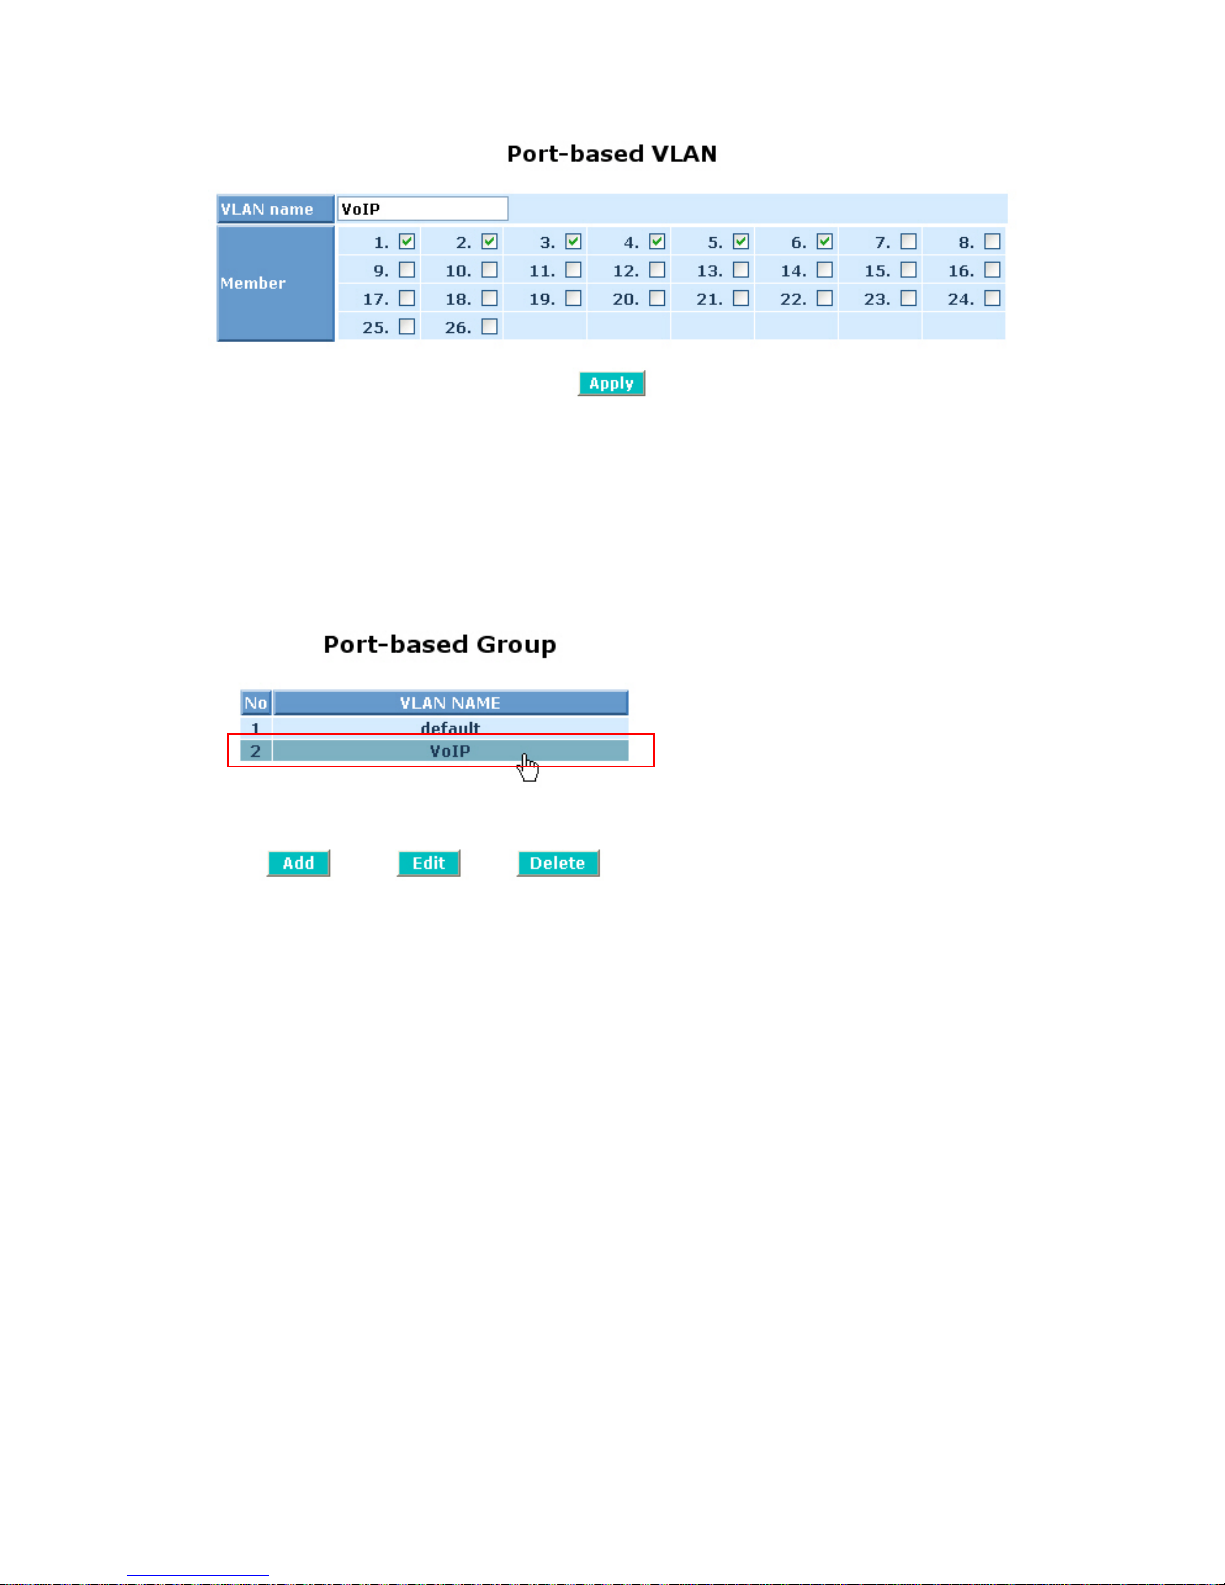
79
Add Group:
Create a new Port-based VLAN. Input the VLAN name and choose the
member by ticking the check box beside the port No., then, press the
<Apply> button to have the setting taken effect.
After Port-based Group created, user can Edit or Delete specified group by
selecting group name
Delete Group:
Just press the <Delete> button to remove the selected group ent ry from
the Port-based group table.
Edit a group:
Just select a group entry and press the <Edit> button, then you can
modify a group‘s description and member set.
Page 88
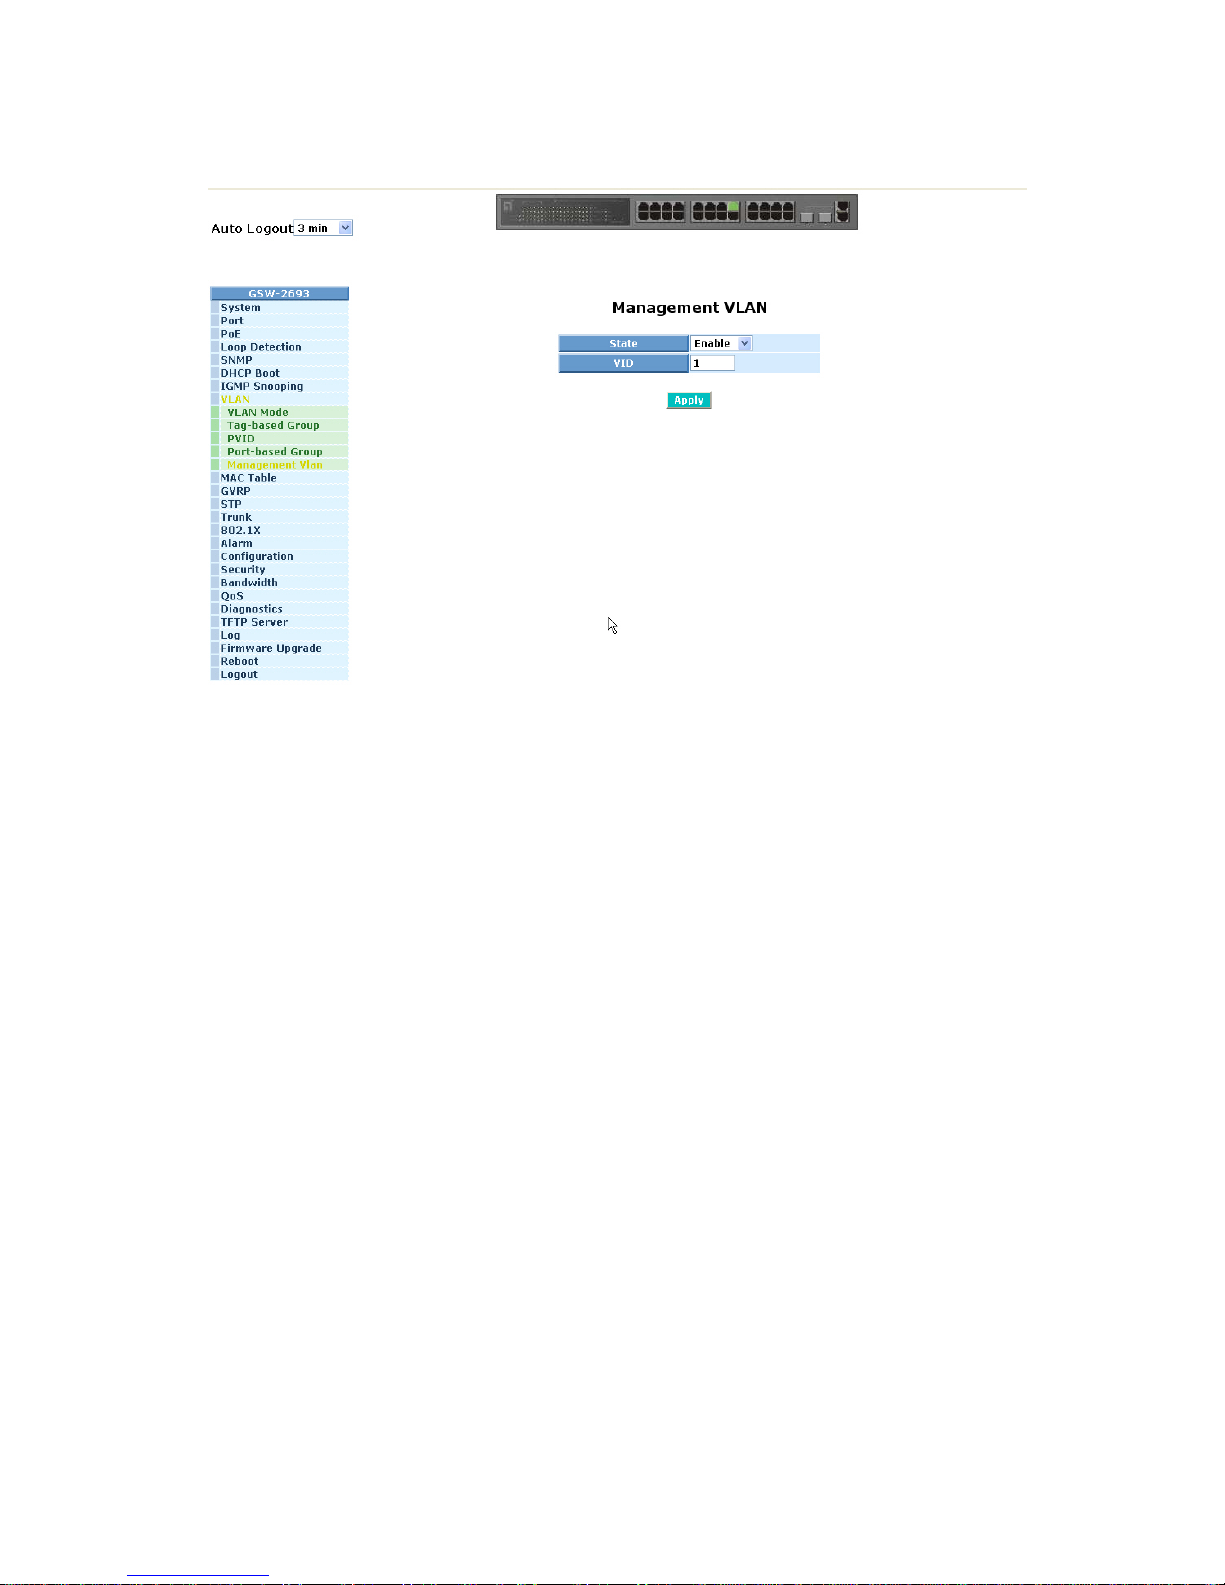
80
3-8-5. Management Vlan
Page 89
81
3-9. MAC Table
MAC Table Configuration gathers many functions, including MAC Table
Information, MAC Table Maintenance, Static and MAC Alias, which cannot be
categorized to some function type. They are described below.
Function name:
MAC Table Information
Function Description:
Display the static or dynamic learning MAC entry and the state for the selected
port.
Parameter description:
Port:
Select the port you would like to inquire.
Search:
Set up the MAC entry you would like to inquire.
The default is ??-??-??-??-??-??
MAC:
Display the MAC address of one entry you selected from the searched
MAC entries table.
Alias:
Set up the Alias for the selected MAC entry.
Set Alias:
Save the Alias of MAC entry you set up.
Search:
Find the entry that meets your setup.
Previous Page:
Move to the previous page.
Next Page:
Move to the next page.
Alias:
The Alias of t he searched entry.
MAC Address:
The MAC address of the searched entry.
Page 90
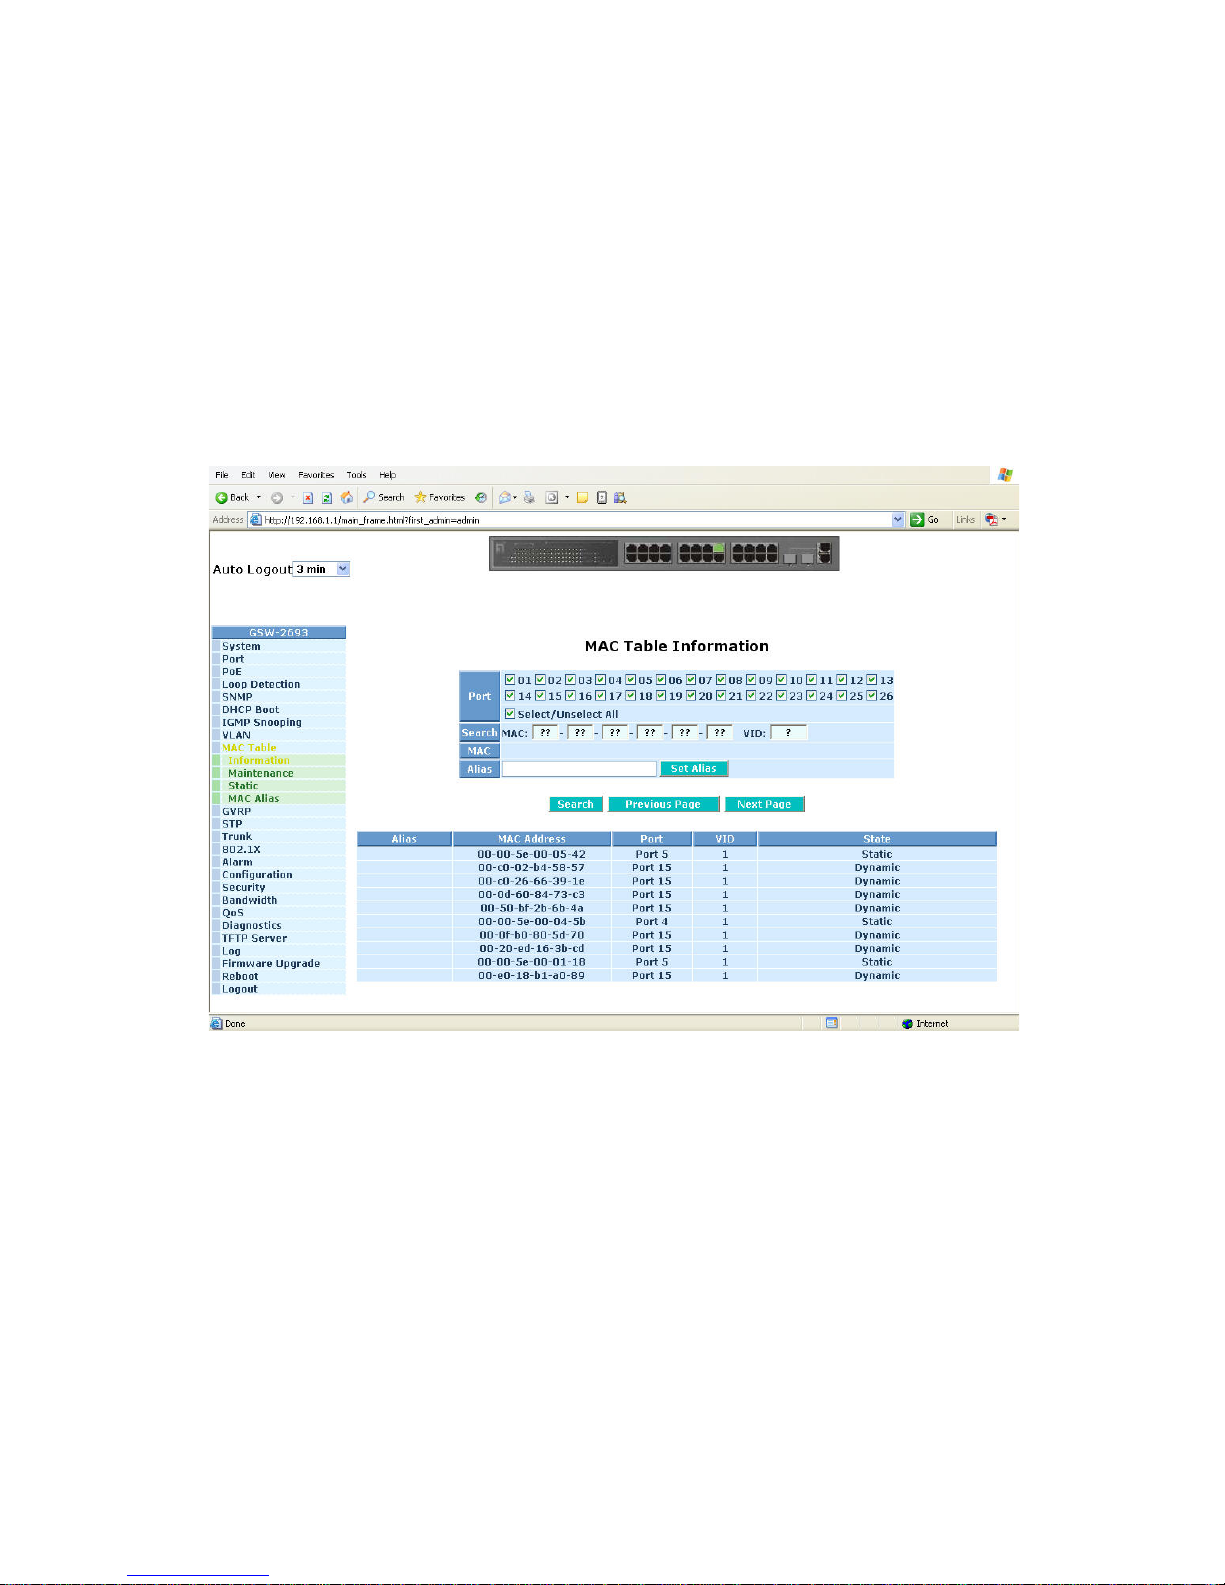
82
Port:
The port that exists in the searched MAC Entry.
VID:
VLAN Group that MAC Entry exists.
State:
Display the method that this MAC Entry is built. It may show “Dynamic
MAC” or “Static MAC”.
Fig. 3-29
Page 91
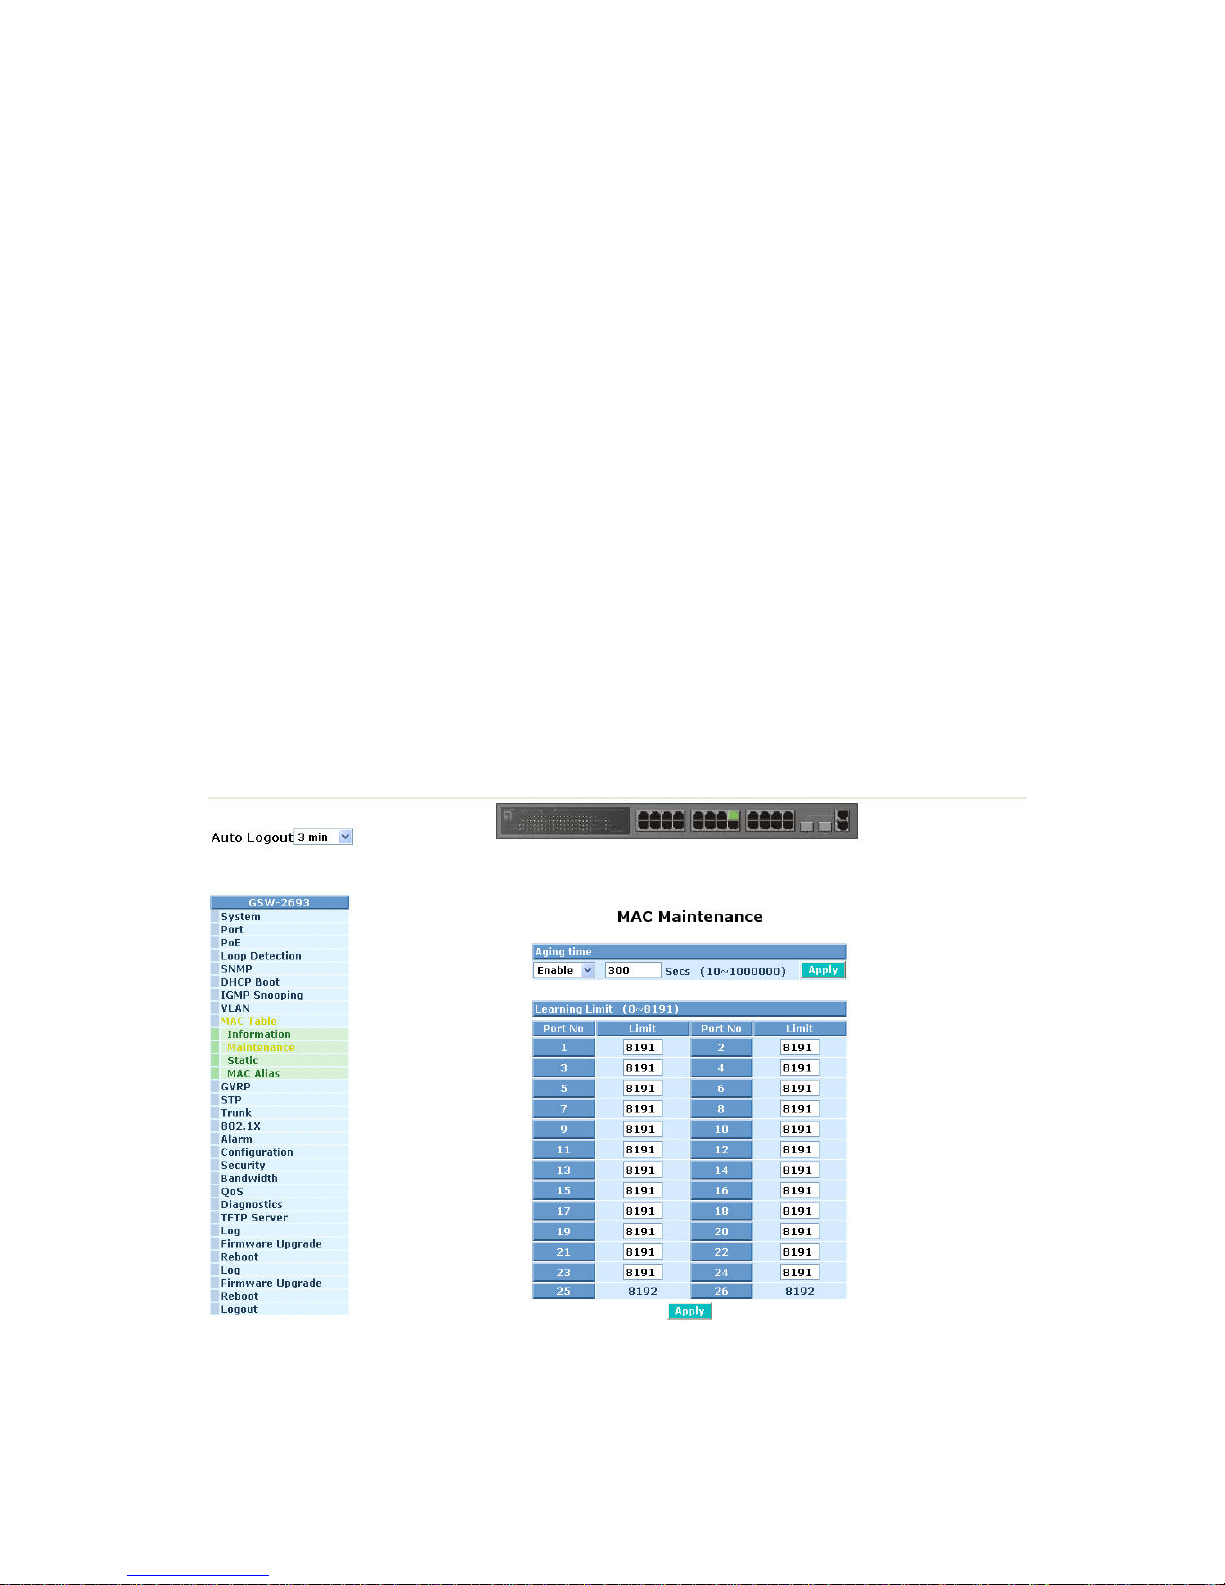
83
Function Name:
MAC Table Maintenance
Function Description:
This function can allow the user to set up the processing mechanism of MAC
Table. An idle MAC address exceeding MAC Address Age-out Time will be
removed from the MAC Table. The range of Age-out Time is 10-1000000
seconds, and the setup of this time will have no effect on static MAC
addresses.
In addition, the learning limit of MAC maintenance is able to limit the amount
of MAC that each port can learn.
Parameter description:
Aging Time:
Delete a MAC address idling for a period of time from the MAC Table,
which will not affect static MAC address. Range of MAC Address Aging
Time is 10-1000000 se conds. The default Aging Time is 300 seconds.
Learning Limit:
To set up the maximum amount of MAC that each port can learn. Valid
value of learning limit for port 1~24 ranges from 0-8191. As to port
25~port 26, only the fixed value “8192” is assigned to these two ports
and user cannot configure this value.
Fig. 3-30
Page 92
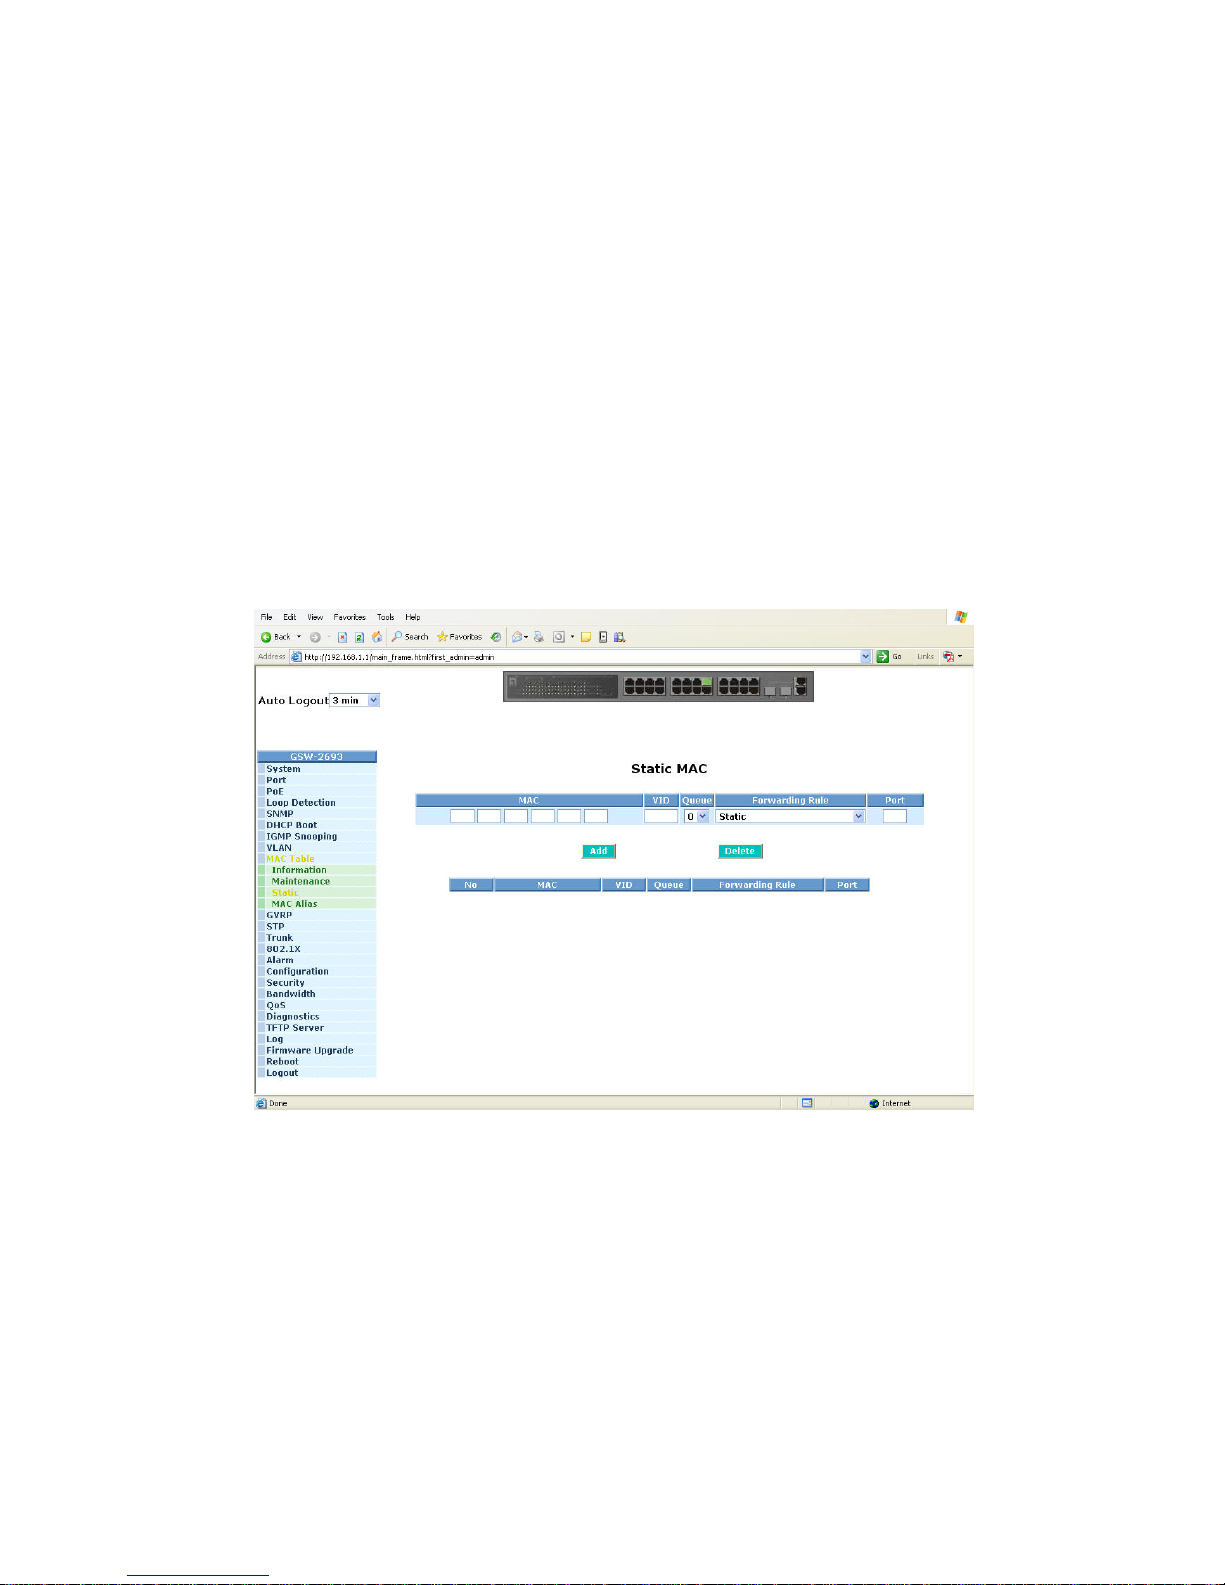
84
Function Name:
Static Setting
Function Description:
The function of Static is used to configure MAC’s real manners inside of the
switch. Three kinds of manners including static, static with destination drop
and static with source drop are contained in this function .
As “static” is chosen, assign a MAC address to a specific port, all of the
switch’s traffics sent to this MAC address will be forwarded to this port.
As “static with destination drop” is chosen, the packet will be dropped if its DA
is equal to the value you set up. Due to this setting belongs to the global one,
so, it may affect all ports’ transmission of the packets.
As “static with source drop” is chosen, the packet will be dropped if its SA is
equal to the value you set up. Due to this setting belongs to the global one, so,
it may affect all ports’ transmission of the packets.
Fig. 3-31
Parameter description:
MAC:
It is a six-byte long Ethernet hardware address and usually expressed by
hex and separated by hyphens. For example,
00 –
11 – 6B - D6 – 00 - 01
VID:
VLAN identifier. This will be filled only when tagged VLAN is applied.
Valid range is 1 ~ 4094.
Page 93
85
Queue (Priority):
Set up the priority( 0~3) for the MAC.
Forwarding Rule(Drop Policy):
Static:
A MAC address is assigned to a specific port, all of the switch’s
traffics sent to this MAC address will be forwarded to this port.
Static with Destination Drop:
While the DA of the incoming packets meets the value you set up,
these packets will be dropped.
Static with Source Drop:
While the SA of the incoming packets meets the value you set up,
these packets will be dropped.
Port :
Select the port No. you would like to do setup in the switch. It is 1 ~26.
Page 94
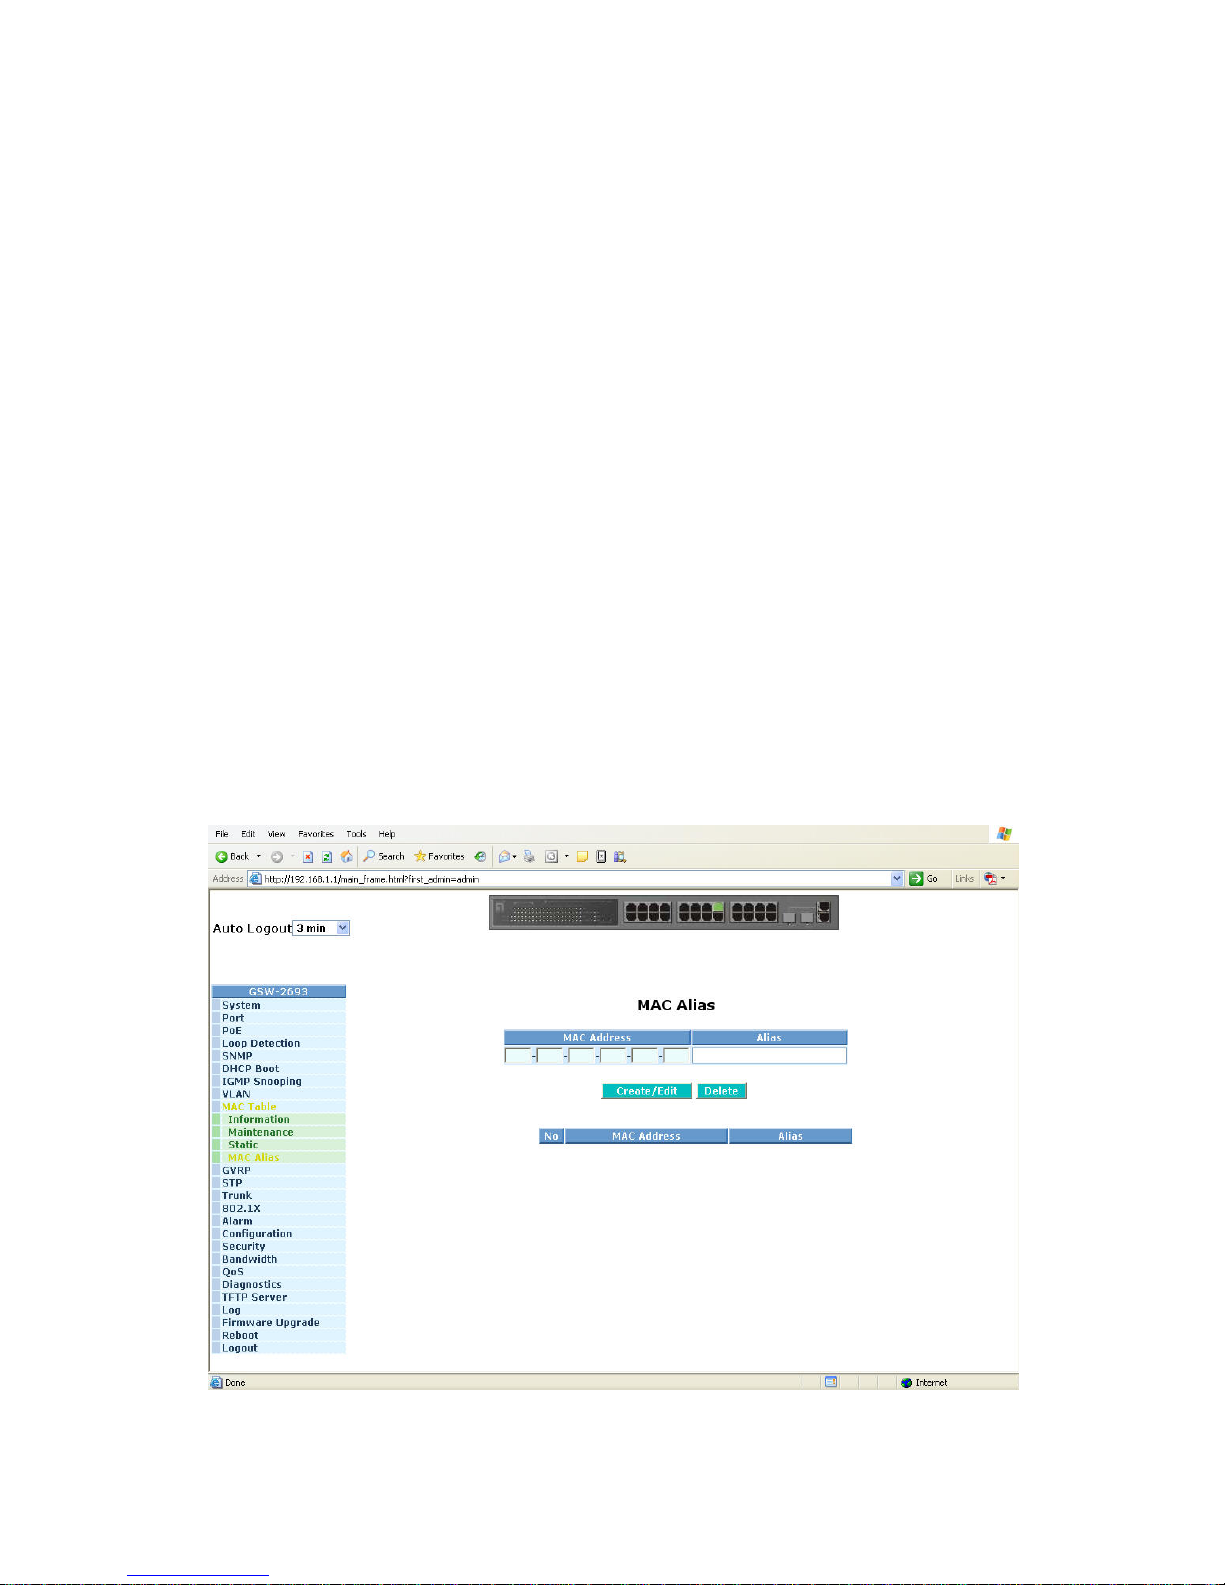
86
Function name:
MAC Alias
Function description:
MAC Alias function is used to let you assign MAC address a plain English
name. This will help you tell which MAC address belongs to which user in the
illegal access report. At the initial time, it shows all pairs of the existed alias
name and MAC address.
There are three MAC alias functions in this function folder, including MAC Alia s
Add, MAC Alias Edit and MAC Alias Delete. You can click <Create/Edit>
button to add/modify a new or an existed alias name for a specified MAC
address, or mark an existed entry to delete it. Alias name must be composed
of A-Z, a-z and 0-9 only and has a maximal length of 15 characters.
Function name:
MAC Alias Create/Edit or Delete
Function description:
In the MAC Alias function, MAC Alias Add/Edit function is used to let you add
or modify an association between MAC address and a plain English name.
User can click <Create/Edit> button to add a new record with name.
As to MAC Alias Delete function is used to let you remove an alias name to a
MAC address. You can select an existed MAC address or alias name to
remove.
Fig. 3-32
Page 95
87
Parameter description:
MAC Address:
It is a six-byte long Ethernet hardware address and usually expressed by
hex and separated by hyphens. For example,
00 –
11 – 6B - D6 – 00 - 02
Alias:
MAC alias name you assign.
Note: If there are too many MAC addresses learned in the table, we recommend
you inputting the MAC address and alias name directly.
Page 96
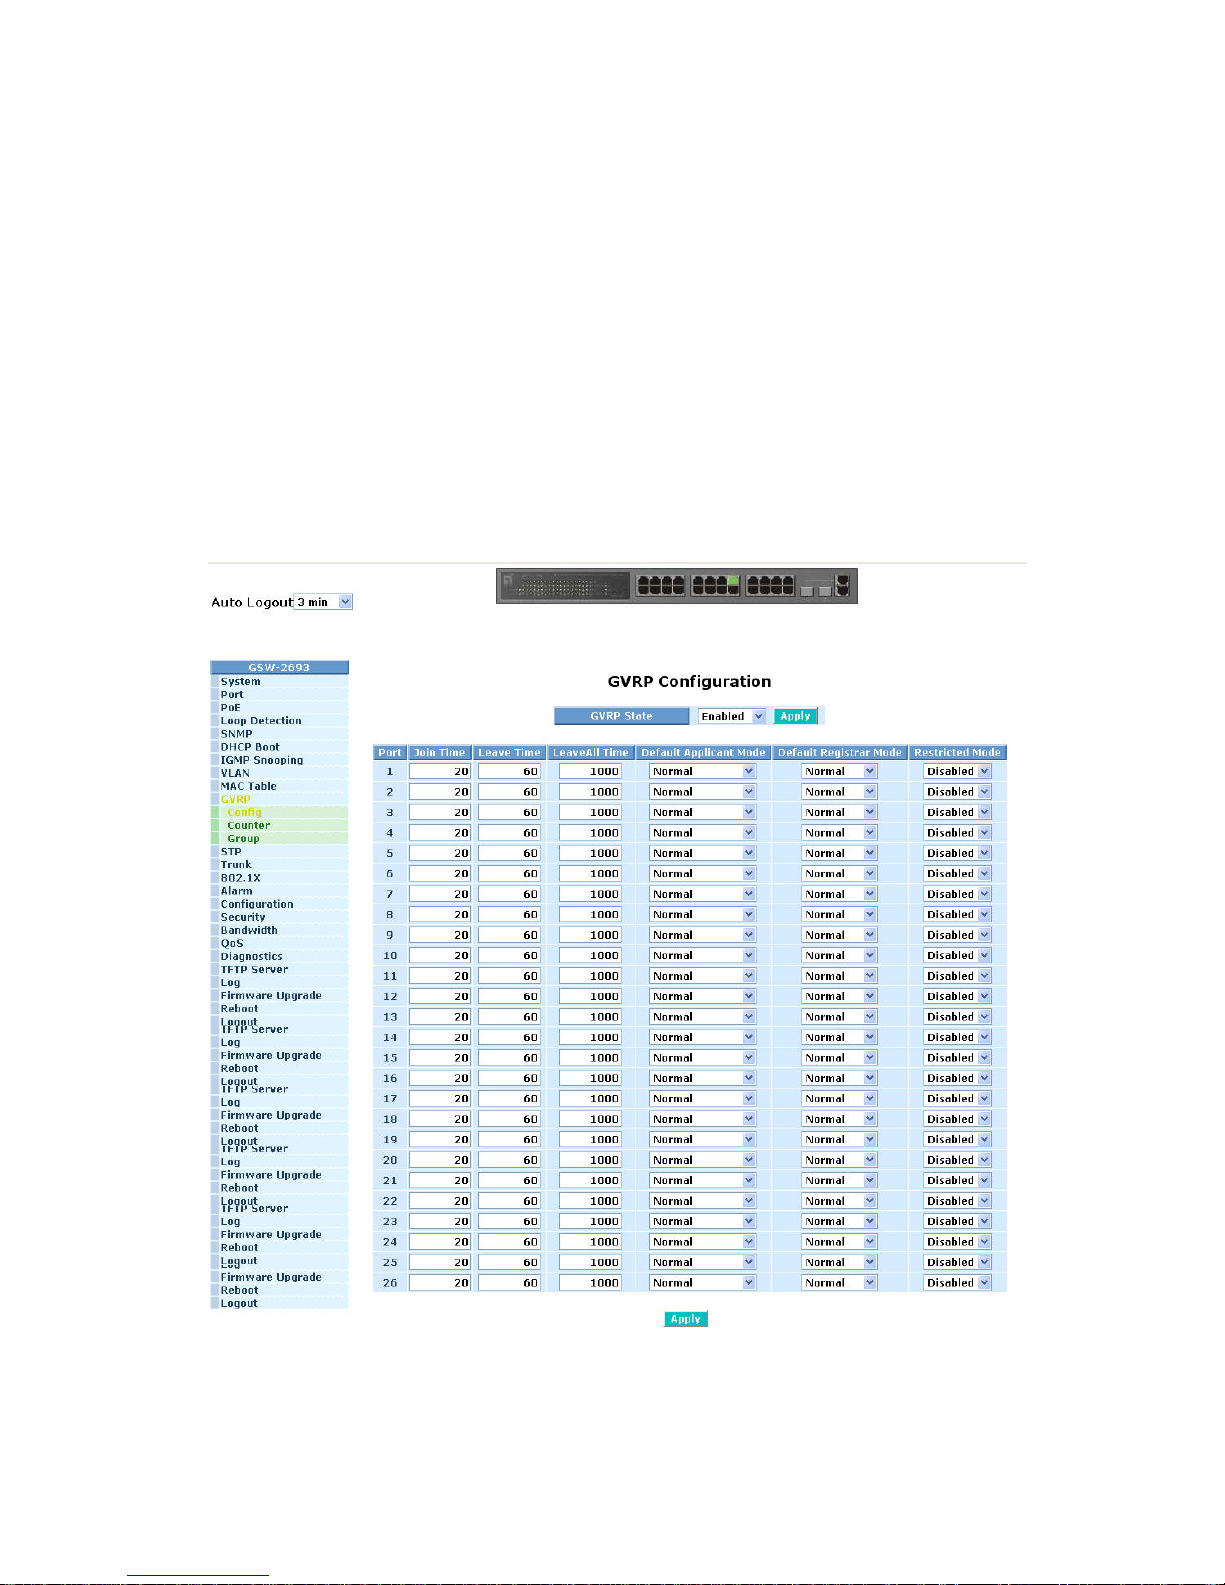
88
3-10. GVRP Configuration
GVRP is an application based on Generic Attribute Registration Protocol
(GARP), mainly used to automatically and dynamically maintain the group
membership information of the VLANs. The GVRP offers the function providing the
VLAN registration service through a GARP application. It makes use of GARP
Information Declaration (GID) to maintain the ports associated with their attribute
database and GARP Information Propagation (GIP) to communicate among
switches and end stations. With GID information and GIP, GVRP state machine
maintain the contents of Dynamic VLAN Registration Entries for each VLAN and
propagate these information to other GVRP-aware devices to setup and update
their knowledge database, the set of VLANs associated with currently active
members, and through which ports these members can be reached.
In GVRP Configuration function folder, there are three functions supported,
including GVRP Config, GVRP Counter and GVRP Group explained below.
Fig. 3-33
Page 97
89
Function name:
GVRP Config
Function description:
In the function of GVRP Config, it is used to configure each port’s GVRP
operation mode, in which there are seven parameters needed to be configured
described below.
Parameter description:
GVRP State Setting:
This function is simply to let you enable or disable GVRP function. You
can pull down the list and click the <Downward> arrow key to choose
“Enable” or “Disable”. Then, click the <Apply> button, the system will
take effect immediately.
Join Time:
Used to declare the Join Time in unit of centisecond. Valid time range:
20 –100 centisecond, Default: 20 centisecond.
Leave Time:
Used to declare the Leave Time in unit of centisecond. Valid time range:
60 –300 centisecond, Default: 60 centisecond.
Leave All Time:
A time period for announcement that all registered device is going to be
de-registered. If someone still issues a new join, then a registration will
be kept in the switch. Valid range: 1000-5000 unit time, Default: 1000 unit
time.
Default Applicant Mode:
The mode here means the type of participant. There are two modes,
normal participant and non-participant, provided for the user’s choice.
Normal:
It is Normal Participant. In this mode, the switch participates
normally in GARP protocol exchanges. The default setting is
Normal.
Non-Participant:
It is Non-Participant. In this mode, the switch does not send or
reply any GARP messages. It just listens messages and
reacts for the received GVRP BPDU.
Default Registrar Mode:
The mode here means the type of Registrar. There are three types of
parameters for registrar administrative control value, normal registrar,
fixed registrar and forbidden registrar, provided for the user’s choice.
Page 98
90
Normal:
It is Normal Registration. The Registrar responds normally to
incoming GARP messages. The defa ult setting is Normal.
Fixed:
It is Registration Fixed. The Registrar ignores all GARP
messages, and all members remain in the registered (IN)
state.
Forbidden:
It is Registration Forbidden. The Registrar igno res all GARP
messages, and all members remain in the unregistered
(EMPTY) state.
Restricted Mode:
This function is used to restrict dynamic VLAN be created when this port
received GVRP PDU. There are two modes, disable and enable,
provided for the user’s choice.
Disabled:
In this mode, the switch dynamic VLAN will be created when
this port received GVRP PDU. The default setting is Normal.
Enabled:
In this mode, the switch does not create dynamic VLAN when
this port received GVRP PDU. Except received dynamic
VLAN message of the GVRP PDU is an existed static VLAN in
the switch, this port will be added into the static VLAN
members dynamically.
Page 99
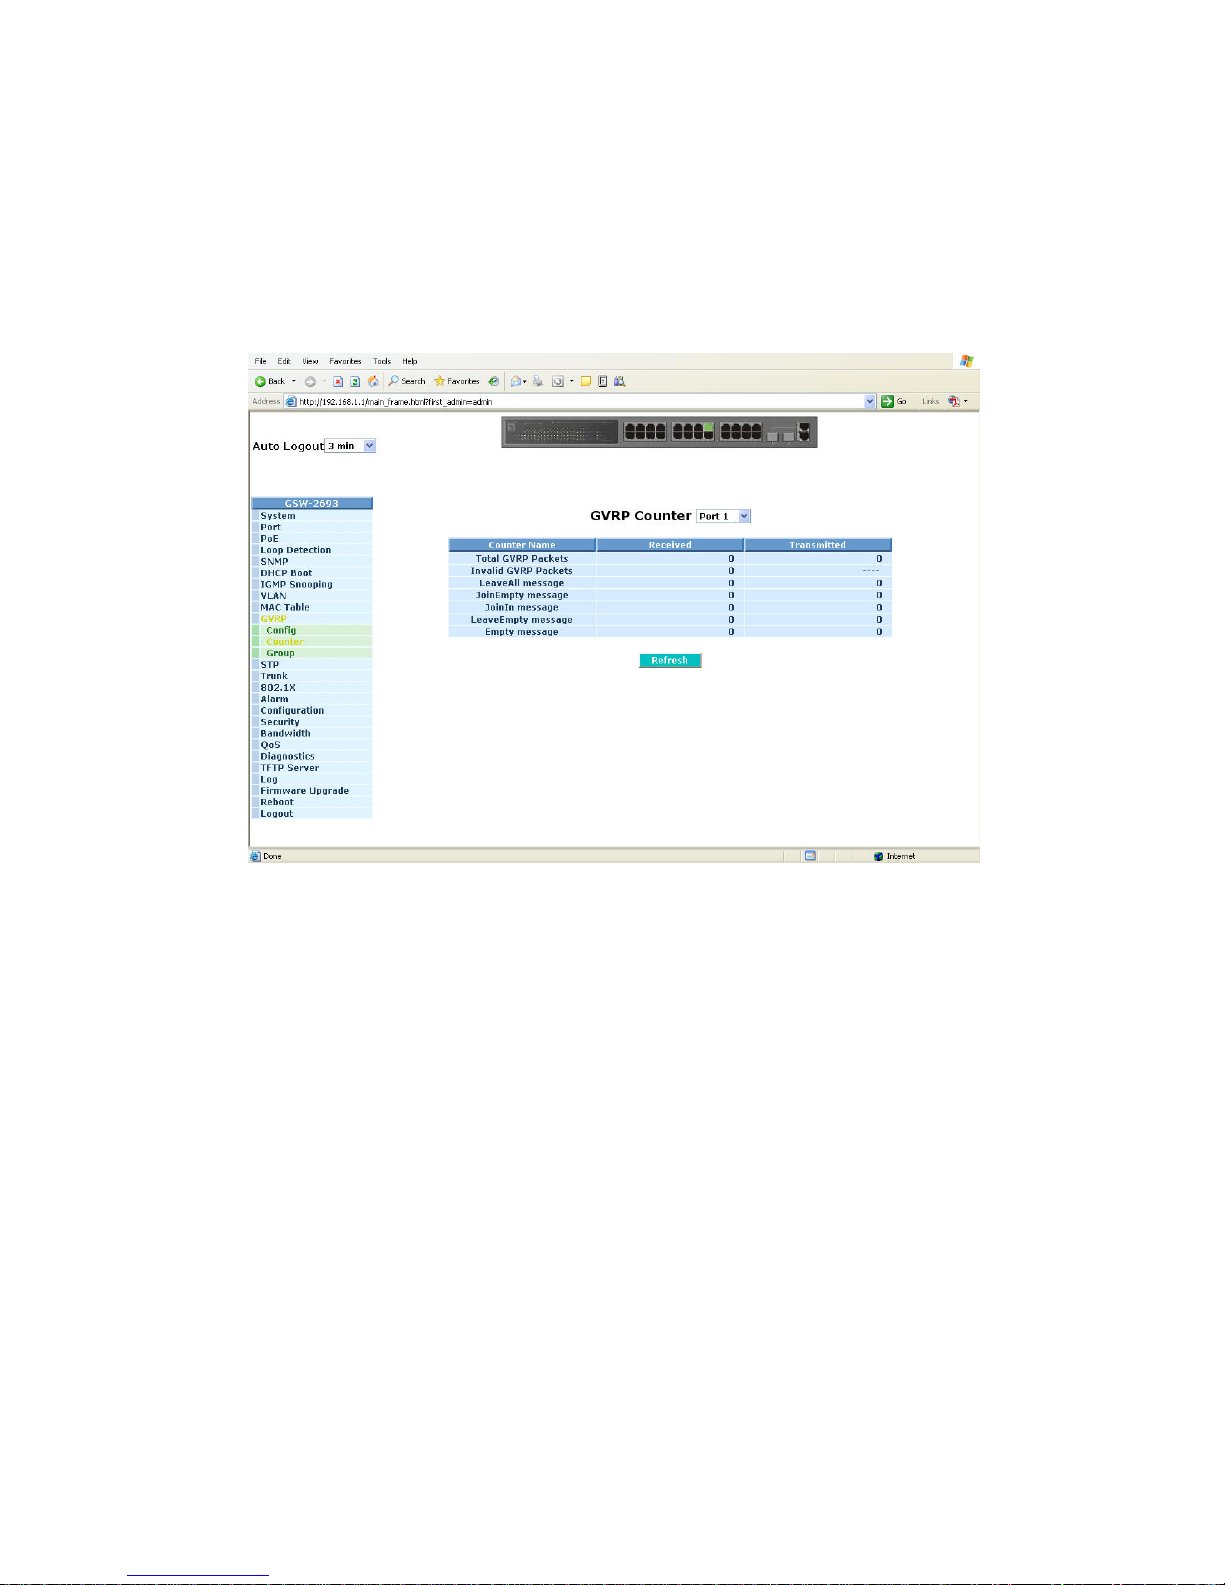
91
Function name:
GVRP Counter
Function description:
All GVRP counters are mainly divided into Received and Transmitted two
categories to let you monitor the GVRP actions. Actually, they are GARP
packets.
Fig. 3-34
Parameter description:
Counter Name:
Total GVRP Packets:
Total GVRP BPDU is received by the GVRP application.
Invalid GVRP Packets:
Number of invalid GARP BPDU is received by the GARP
application.
LeaveAll Message Packets:
Number of GARP BPDU with Leave All message is received by the
GARP application.
JoinEmpty Message Packets:
Number of GARP BPDU with Join Empty message is received by
the GARP application.
JoinIn Message Packets:
Number of GARP BPDU with Join In message is received by the
GARP application.
Page 100
92
LeaveEmpty Message Packets:
Number of GARP BPDU with Leave Empty message is received by
the GARP application.
Empty Message Packets:
Number of GARP BPDU with Empty message is received by the
GARP application.
Received:
Total GVRP Packets:
Total GARP BPDU is received by the GVRP application.
Invalid GVRP Packets:
Number of invalid GARP BPDU is received by the GVRP
application.
LeaveAll Message Packets:
Number of GARP BPDU with Leave All message is received by the
GARP application.
JoinEmpty Message Packets:
Number of GARP BPDU with Join Empty message is received by
the GARP application.
JoinIn Message Packets:
Number of GARP BPDU with Join In message is received by the
GARP application.
LeaveEmpty Message Packets:
Number of GARP BPDU with Leave Empty message is received by
the GARP application.
Empty Message Packets:
Number of GARP BPDU with Empty message is received by the
GARP application.
Transmitted:
Total GVRP Packets:
Total GARP BPDU is transmitted by the GVRP application.
Invalid GVRP Packets:
Number of invalid GARP BPDU is transmitted by the GVRP
application.
LeaveAll Message Packets:
Number of GARP BPDU with Leave All message is transmitted by
the GARP application.
JoinEmpty Message Packets:
Number of GARP BPDU with Join Empty message is transmitted by
the GARP application.
JoinIn Message Packets:
Number of GARP BPDU with Join In message is transmitted by the
GARP application.
LeaveEmpty Message Packets:
Number of GARP BPDU with Leave Empty message is transmitted
by the GARP application.
Empty Message Packets:
Number of GARP BPDU with Empty message is transmitted by the GARP
application.
 Loading...