

Page 1
LevelOne
GSW-1290
4-port 1000T/mini GBIC + 2 expandable slots
L2 SNMP Gigabit Switch
User`s Manual
Page 2

Copyright
The contents of this publication may not be reproduced in any part or as a whole,
stored, transcribed in an information retrieval system, translated into any
language, or transmitted in any form or by any means, mechanical, magnetic,
electronic, optical, photocopying, manual, or otherwise, without the prior written
permission.
Trademarks
All product, company, brand names are trademarks or registered trademarks of
their respective companies. They are used for identification purpose only.
Specifications are subject to be changed without prior notice.
FCC Interference Statement
This equipment has been tested and found to comply with the limits for a Class
B digital device pursuant to Part 15 of the FCC Rules. These limits are designed
to provide reasonable protection against radio interference in a commercial
environment. This equipment can generate, use and radiate radio frequency
energy and, if not installed and used in accordance with the instructions in this
manual, may cause harmful interference to radio communications. Operation of
this equipment in a residential area is likely to cause interference, in which case
the user, at his own expense, will be required to take whatever measures are
necessary to correct the interference.
CE Declaration of Conformity
This equipment complies with the requirements relating to electromagnetic
compatibility, EN 55022/A1 Class B, and EN 50082-1. This meets the essential
protection requirements of the European Council Directive 89/336/EEC on the
approximation of the laws of the member states relation to electromagnetic
compatibility.
Page 3
Table of Contents
About This Manual .............................................................................................................. vii
Intended Readers ..............................................................................................................................................................vii
Typographical Conventions..............................................................................................................................................vii
Notes, Notices, and Cautions.......................................................................................................................................... viii
Safety Instructions .............................................................................................................. viii
Introduction ..........................................................................................................................11
Switch Description...............................................................................................................11
Features ..............................................................................................................................11
Front Panel Components ....................................................................................................13
LED Indicators .................................................................................................................................................................13
Stacking LED Indicators...................................................................................................................................................14
Rear Panel Description .......................................................................................................14
Plug-in Modules ..................................................................................................................15
MDU-1290T 1000BASE-T Module...................................................................................................................................15
MDU-1290M SFP (Mini GBIC) Module ..........................................................................................................................15
MDU-1290S IEEE 1394 Stacking Module........................................................................................................................16
Switch Stacking...................................................................................................................16
Management Options..........................................................................................................17
Installation ............................................................................................................................19
Package Contents...............................................................................................................19
Before You Connect to the Network.................................................................................... 19
Installing the Switch without the Rack..............................................................................................................................20
Installing the Switch in a Rack .........................................................................................................................................20
Connecting Stacked Switch Groups..................................................................................................................................23
Configuring a Switch Group for Stacking.........................................................................................................................25
Connecting the Console Port............................................................................................................................................28
Password Protection.........................................................................................................................................................28
SNMP Settings..................................................................................................................................................................29
IP Address Assignment .....................................................................................................................................................30
Connecting Devices to the Switch.....................................................................................................................................32
Basic Switch Management ..................................................................................................33
Before You Start..................................................................................................................33
Web-based User Interface ..................................................................................................34
Areas of the User Interface...............................................................................................................................................34
Login to Web Manager .....................................................................................................................................................35
Web Pages and Folders....................................................................................................................................................35
Switch Information ...........................................................................................................................................................36
Switch IP Settings ...............................................................................................................36
Security IP Management Stations Configuration .............................................................................................................38
User Account Management................................................................................................. 40
Admin and User Privileges...............................................................................................................................................41
Save Changes.....................................................................................................................41
Factory Reset......................................................................................................................42
Restart System ..................................................................................................................................................................43
Advanced Settings.............................................................................................................................................................44
Page 4
Stack Information ................................................................................................................46
System Configuration ..........................................................................................................49
Port Configuration ...............................................................................................................50
Port Mirroring ......................................................................................................................51
Traffic Control......................................................................................................................52
Link Aggregation .................................................................................................................53
LACP Port Settings...........................................................................................................................................................55
IGMP ...................................................................................................................................56
IGMP Snooping ................................................................................................................................................................56
Static Router Ports Entry..................................................................................................................................................58
Spanning Tree.....................................................................................................................59
Switch Spanning Tree Settings..........................................................................................................................................60
STP Port Settings..............................................................................................................................................................63
Forwarding & Filtering ......................................................................................................... 65
Unicast Forwarding .........................................................................................................................................................65
Multicast Forwarding.......................................................................................................................................................66
Multicast Port Filtering Mode..........................................................................................................................................67
VLANs .................................................................................................................................68
802.1Q Static VLANs........................................................................................................................................................71
GVRP Setting....................................................................................................................................................................74
QoS .....................................................................................................................................76
802.1p Default Priority.....................................................................................................................................................76
802.1p User Priority.........................................................................................................................................................77
QoS Output Scheduling Configuration .............................................................................................................................77
Traffic Segmentation.........................................................................................................................................................78
Bandwidth Control ...........................................................................................................................................................80
MAC Notification .................................................................................................................81
Global Settings .................................................................................................................................................................81
Port Settings .....................................................................................................................................................................82
System Log Server..............................................................................................................83
Port Security........................................................................................................................85
SNTP Settings.....................................................................................................................86
Current Time and SNTP Settings......................................................................................................................................86
Time Zone and DST..........................................................................................................................................................87
Access Profile Table ...........................................................................................................89
Security Management ..........................................................................................................97
Trusted Host........................................................................................................................97
Port Access Entity ............................................................................................................... 98
802.1X Authenticator Settings ........................................................................................................................................100
PAE System Control .......................................................................................................................................................103
Radius Server..................................................................................................................................................................106
SNMP Management ............................................................................................................108
SNMPV3 ...........................................................................................................................108
SNMP User Table...........................................................................................................................................................108
SNMP View Table...........................................................................................................................................................111
SNMP Group Table ........................................................................................................................................................112
SNMP Community Table ................................................................................................................................................114
SNMP Host Table...........................................................................................................................................................116
SNMP Engine ID ............................................................................................................................................................117
Page 5
Network and System Monitoring.......................................................................................118
Port Utilization ...................................................................................................................120
Packets .............................................................................................................................121
Received Packets ............................................................................................................................................................121
Received Unicast/Multicast/Broadcast Packets..............................................................................................................122
Transmitted Packets .......................................................................................................................................................124
Errors ................................................................................................................................125
Received Errors..............................................................................................................................................................126
Transmitted Errors .........................................................................................................................................................128
Packet Size......................................................................................................................................................................130
MAC Address .................................................................................................................... 131
Switch History ...................................................................................................................133
IGMP Snooping.................................................................................................................134
Browser Router Port.......................................................................................................... 135
VLAN Status......................................................................................................................136
Session Table ...................................................................................................................136
Authenticator State............................................................................................................137
System Maintenance..........................................................................................................138
TFTP Services ..................................................................................................................138
Download Firmware.......................................................................................................................................................138
Download Configuration File.........................................................................................................................................139
Save Settings...................................................................................................................................................................139
Save History Log ............................................................................................................................................................139
Ping Test ...........................................................................................................................140
Save Changes...................................................................................................................140
Factory Reset....................................................................................................................141
Restart System..................................................................................................................141
Logout.............................................................................................................................................................................142
Technical Specifications ...................................................................................................143
Page 6
Page 7

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
About This Manual
This manual is divided into two general sections:
Chapters 1-3 provide Basic Setup information. This is where you will find a general introduction to the Switch,
its hardware and management features, as well as a guide to setting up the Switch hardware and initial
configuration.
Chapters 4-8 discuss Advanced Configuration topics. These chapters describe management and configuration
of Switch features, following the layout of the Switch’s Web Manager. Each of the Switch’s six main folders—
Configuration, Security, Management, Monitoring, Maintenance, and Single IP Management—has a separate
chapter devoted to it.
Intended Readers
The GSW-1290 User Manual contains information useful for setup and management and of the LevelOne GSW1290 Switch. This manual is intended for network managers familiar with network management concepts and
terminology.
Typographical Conventions
Convention Description
[ ]
In a command line, square brackets indicate an optional entry. For example:
[copy filename] means that optionally you can type copy followed by the
name of the file. Do not type the brackets.
Bold font
Indicates a button, a toolbar icon, menu, or menu item. For example: Open
the File menu and choose Cancel. Used for emphasis. May also indicate
system messages or prompts appearing on your screen. For example: You
have mail. Bold font is also used to represent filenames, program names
and commands. For example: use the copy command.
Boldface Typewriter
Font
Indicates commands and responses to prompts that must be typed exactly as
printed in the manual.
Initial capital letter
Indicates a window name. Names of keys on the keyboard have initial
capitals. For example: Click Enter.
Italics
Indicates a window name or a field. Also can indicate a variables or
parameter that is replaced with an appropriate word or string. For example:
type filename means that you should type the actual filename instead of the
word shown in italic.
Menu Name > Menu Option
Indicates the menu structure. Device > Port > Port Properties means the
Port Properties menu option under the Port menu option that is located
under the Device menu.
vii
Page 8
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Notes, Notices, and Cautions
NOTE: A NOTE indicates important information that helps you make
better use of your device.
NOTICE: A NOTICE indicates either potential damage to hardware or loss
of data and tells you how to avoid the problem.
CAUTION: A CAUTION indicates a potential for property damage,
personal injury, or death.
Safety Instructions
Use the following safety guidelines to ensure your own personal safety and to help protect your system from
potential damage. Throughout this safety section, the caution icon ( ) is used to indicate cautions and
precautions that you need to review and follow.
Safety Cautions
To reduce the risk of bodily injury, electrical shock, fire, and damage to the equipment, observe the following
precautions.
Observe and follow service markings. Do not service any product except as explained in your system
documentation. Opening or removing covers that are marked with the triangular symbol with a lightning bolt
may expose you to electrical shock. Components inside these compartments should be serviced only by a trained
service technician.
If any of the following conditions occur, unplug the product from the electrical outlet and replace the part or
contact your trained service provider:
• The power cable, extension cable, or plug is damaged.
• An object has fallen into the product.
• The product has been exposed to water.
• The product has been dropped or damaged.
• The product does not operate correctly when you follow the operating instructions.
Keep your system away from radiators and heat sources. Also, do not block cooling vents.
Do not spill food or liquids on your system components, and never operate the product in a wet environment. If
the system gets wet, see the appropriate section in your troubleshooting guide or contact your trained service
provider.
Do not push any objects into the openings of your system. Doing so can cause fire or electric shock by shorting
out interior components.
viii
Use the product only with approved equipment.
Page 9
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Allow the product to cool before removing covers or touching internal components.
Operate the product only from the type of external power source indicated on the electrical ratings label. If you
are not sure of the type of power source required, consult your service provider or local power company.
To help avoid damaging your system, be sure the voltage selection Switch (if provided) on the power supply is
set to match the power available at your location:
• 115 volts (V)/60 hertz (Hz) in most of North and South America and some Far Eastern countries such as
South Korea and Taiwan
• 100 V/50 Hz in eastern Japan and 100 V/60 Hz in western Japan
• 230 V/50 Hz in most of Europe, the Middle East, and the Far East
Also be sure that attached devices are electrically rated to operate with the power available in your location.
Use only approved power cable(s). If you have not been provided with a power cable for your system or for any
AC-powered option intended for your system, purchase a power cable that is approved for use in your country.
The power cable must be rated for the product and for the voltage and current marked on the product's electrical
ratings label. The voltage and current rating of the cable should be greater than the ratings marked on the product.
NOTE: A qualified electrician must perform all connections to DC power
and to safety grounds. All electrical wiring must comply with applicable
local or national codes and practices.
To help prevent electric shock, plug the system and peripheral power cables into properly grounded electrical
outlets. These cables are equipped with three-prong plugs to help ensure proper grounding. Do not use adapter
plugs or remove the grounding prong from a cable. If you must use an extension cable, use a 3-wire cable with
properly grounded plugs.
Observe extension cable and power strip ratings. Make sure that the total ampere rating of all products plugged
into the extension cable or power strip does not exceed 80 percent of the ampere ratings limit for the extension
cable or power strip.
To help protect your system from sudden, transient increases and decreases in electrical power, use a surge
suppressor, line conditioner, or uninterruptible power supply (UPS).
Position system cables and power cables carefully; route cables so that they cannot be stepped on or tripped over.
Be sure that nothing rests on any cables.
Do not modify power cables or plugs. Consult a licensed electrician or your power company for site
modifications. Always follow your local/national wiring rules.
When connecting or disconnecting power to hot-pluggable power supplies, if offered with your system, observe
the following guidelines:
• Install the power supply before connecting the power cable to the power supply.
• Unplug the power cable before removing the power supply.
• If the system has multiple sources of power, disconnect power from the system by unplugging ALL
power cables from the power supplies.
Move products with care; ensure that all casters and/or stabilizers are firmly connected to the system. Avoid
sudden stops and uneven surfaces.
General Precautions for Rack-Mountable Products
Observe the following precautions for rack stability and safety. Also refer to the rack installation documentation
accompanying the system and the rack for specific caution statements and procedures.
Systems are considered to be components in a rack. Thus, "component" refers to any system as well as to various
peripherals or supporting hardware.
ix
Page 10

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
CAUTION: Installing systems in a rack without the front and side stabilizers installed
could cause the rack to tip over, potentially resulting in bodily injury under certain
circumstances. Therefore, always install the stabilizers before installing components in
the rack.
After installing system/components in a rack, never pull more than one component out
of the rack on its slide assemblies at one time. The weight of more than one extended
component could cause the rack to tip over and may result in serious injury.
• Before working on the rack, make sure that the stabilizers are secured to the rack, extended to the floor,
and that the full weight of the rack rests on the floor. Install front and side stabilizers on a single rack or
front stabilizers for joined multiple racks before working on the rack.
• Always load the rack from the bottom up, and load the heaviest item in the rack first.
• Make sure that the rack is level and stable before extending a component from the rack.
• Use caution when pressing the component rail release latches and sliding a component into or out of a
rack; the slide rails can pinch your fingers.
• After a component is inserted into the rack, carefully extend the rail into a locking position, and then
slide the component into the rack.
• Do not overload the AC supply branch circuit that provides power to the rack. The total rack load
should not exceed 80 percent of the branch circuit rating.
• Ensure that proper airflow is provided to components in the rack.
• Do not step on or stand on any component when servicing other components in a rack.
CAUTION: The system chassis must be positively grounded to the rack cabinet frame.
Do not attempt to connect power to the system until grounding cables are connected. A
qualified electrical inspector must inspect completed power and safety ground wiring.
An electrical shock hazard will exist if the safety ground cable is omitted or
disconnected.
CAUTION: Never defeat the ground conductor or operate the equipment in the
absence of a suitably installed ground conductor. Contact the appropriate electrical
inspection authority or an electrician if you are uncertain that suitable grounding is
available.
Protecting Against Electrostatic Discharge
Static electricity can harm delicate components inside your system. To prevent static damage, discharge static
electricity from your body before you touch any of the electronic components, such as the microprocessor. You
can do so by periodically touching an unpainted metal surface on the chassis.
You can also take the following steps to prevent damage from electrostatic discharge (ESD):
When unpacking a static-sensitive component from its shipping carton, do not remove the component from the
antistatic packing material until you are ready to install the component in your system. Just before unwrapping
the antistatic packaging, be sure to discharge static electricity from your body.
When transporting a sensitive component, first place it in an antistatic container or packaging.
Handle all sensitive components in a static-safe area. If possible, use antistatic floor pads and workbench pads
and an antistatic grounding strap.
x
Page 11
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Chapter 1
Introduction
Switch Description
Features
Front Panel Components
LED Indicators
Stacking LED Indicators
Rear Panel Description
Plug-in Modules
Switch Stacking
Management Options
Switch Description
The GSW-1290 is a modular Gigabit Ethernet backbone Switch designed for adaptability and scalability.
The Switch provides a management platform and uplink to backbone for a stacked group of up to twelve
GSW-2492 Switches in a star topology arrangement. Alternatively, the Switch can utilize up to twelve
Gigabit Ethernet ports to function as a central distribution hub for other Switches or Switch groups, or
routers. The four built-in combination Gigabit ports have the option of being used as either 1000BASE-T or
SFP Gigabit connections
Features
• Four built-in combination 10/100/1000BASE-T/SFP ports
• Two additional 4-port modules can be added to stack up to eight additional Switches (IEEE 1394) or up to
eight additional Gigabit Ethernet ports (1000BASE-T or SFP) or use combination of stacking and Gigabit
Ethernet ports.
• Four built-in 1000Base-T ports allow four GSW-2492 to stack.
• Star topology Switch stacking configuration for up to 12 additional GSW-2492 Switches.
• 24 Gbps Switching fabric capacity
• Supports 802.1D STP and 802.1w Rapid Spanning Tree for redundant back up bridge paths
• Supports 802.1Q VLAN
• Supports IGMP snooping
• Supports 802.1p Priority Queues and 802.3ad LACP Link Aggregation.
• Access Control Profile (ACL)
• Multi-layer Access Control (based on MAC address, IP address, VLAN, Protocol, 802.1p, DSCP)
• Quality of Service (QoS) customized control
• Port Security (MAC address table lock) and administrator-definable port security
• 802.1x (port-based and MAC-based) access control and RADIUS Client support
• Per-port bandwidth control
• Broadcast, Multicast and DLF storm control
• IEEE 802.3z and IEEE 802.3x compliant Flow Control for all Gigabit ports
• SNMP v.1, v.2, v.3 network management, RMON support
• Supports optional external Redundant Power Supply
• Flexible management platforms include web-based GUI manager, CLI commands via console or Telnet
• Supports BOOTP/DHCP/DNS Relay
• Supports TFTP upgrade
• Supports System Log
• Simple Network Time Protocol
11
Page 12
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
• MAC address update notification
• Web GUI Traffic Monitoring
• Supports Single IP Management v.1.0
• Supports Traffic Segmentation
12
Page 13
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Front Panel Components
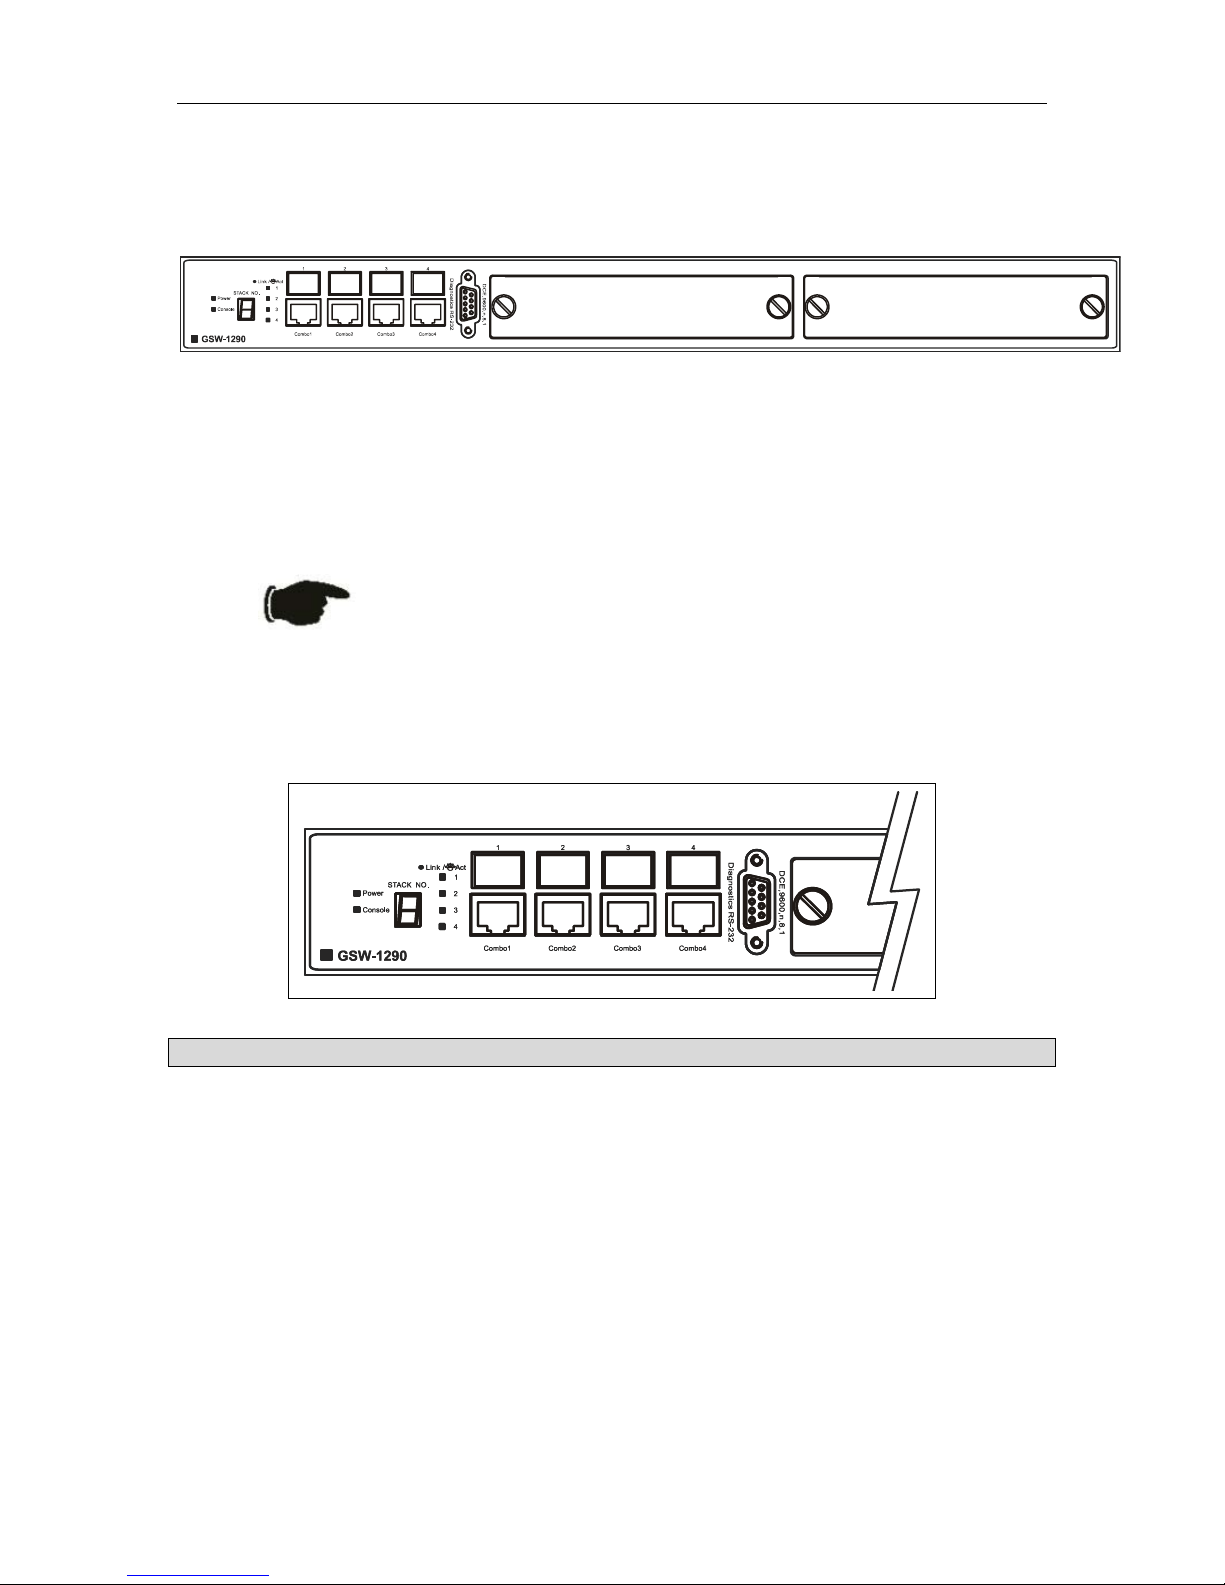
The front panel of the Switch consists of LED indicators, an RS-232 communication port, two slide-in
module slots, and four 1000BASE-T/SFP combination “Combo” ports.
Figure 1-1. Front Panel View of the Switch as shipped (no modules are installed)
Comprehensive LED indicators display the status of the Switch and the network.
An RS-232 DCE console port for setting up and managing the Switch via a connection to a console
terminal or PC using a terminal emulation program.
A front-panel slide-in module slot for Gigabit Ethernet ports can accommodate a 4-port 1000BASE-T
Gigabit Ethernet module, a 4-port Gigabit Ethernet SFP module, or a stacking module to connect to four
GSW-2492 Switches.
NOTICE: The Stack ID LED on the Switch’s front panel will display an F,
regardless of the Switch’s stacking mode (Master Switch in a Switch stack,
or Standalone mode).
LED Indicators
The LED indicators of the Switch include Power, Console, and Link/Act. The following shows the LED
indicators for the Switch along with an explanation of each indicator.
Figure 1-2. LED Indicators
LED Description
This indicator on the front panel should be lit during the Power-On Self Test (POST).
Power
Console
It will light green approximately two seconds after the Switch is powered on to
indicate the ready state of the device.
This indicator is lit green when the Switch is being managed via out-of-band/local
console management through the RS-232 console port using a straight-through
serial cable.
Each on-board Gigabit Ethernet port has a corresponding indicator. This will light
Link/Act
steady green for a valid link and blink whenever there is reception or transmission
(i.e. Activity--Act) of data occurring at a port.
13
Page 14
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
See below for description of Stack ID LED indicator.
Stacking LED Indicators
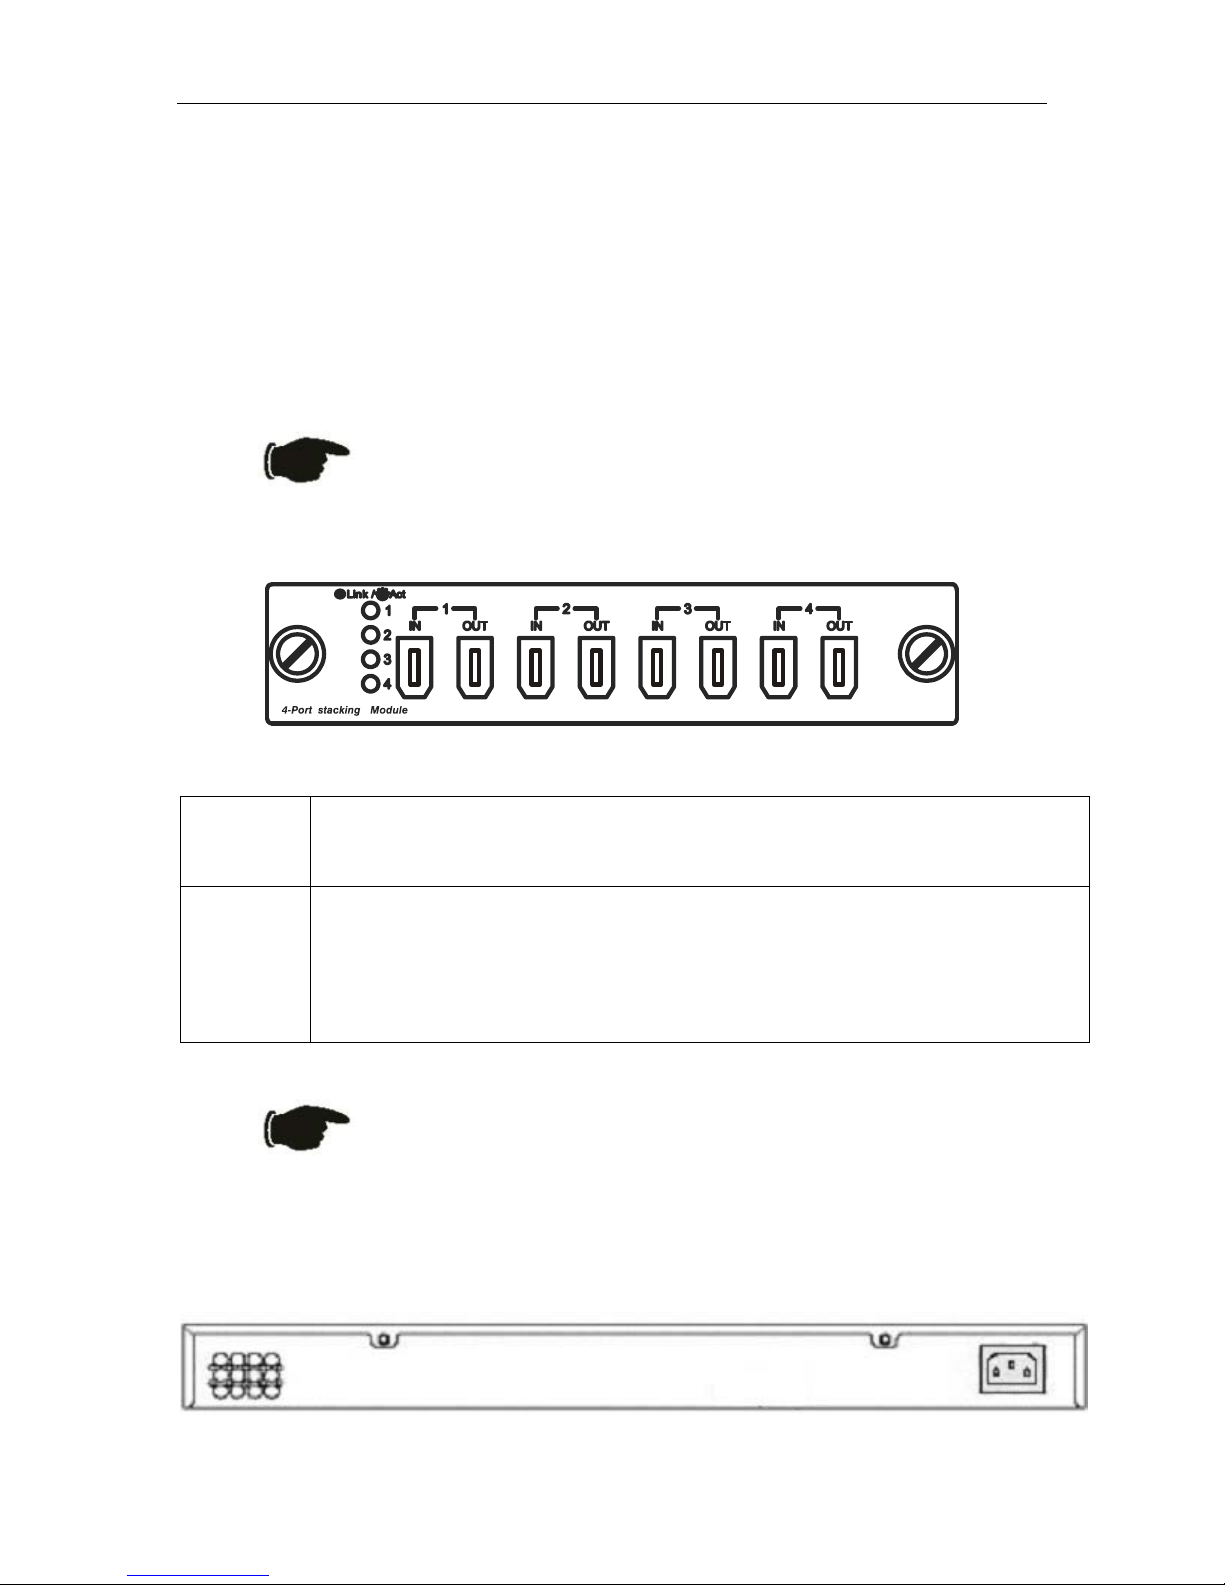
Stacking LED indicators include the Stack ID indicator on the front panel and the Link/Act indicators on
the front of the MDU-1290S stacking module.
Each stacking module has a single Link/Act LED indicator on its front panel for each IEEE 1394 IN/OUT
pair
Figure 1-3. Front panel of MDU-1290S IEEE 1394 stacking module
NOTICE: The four build-in combination ports on the front panel of the
GSW-1290 can be configured as stacking ports using the CLI.
The Link/Act LEDs have the same function as the corresponding LEDs for the Switch’s
Link/Act
Stack ID
built-in Gigabit Ethernet ports. The Link LED lights to confirm a valid link, while the Act
LED blinks to indicate activity on the link.
The Switch includes a digital indicator to indicate the Switch status in a stacked Switch
group. An “F” indicates the Switch is acting in the capacity of a master Switch of a stacked
group of GSW-1290/GSW-2492 Switches. The remaining slave Switches in the group will
display a corresponding stack number (1-C) to indicate the logical position of the slave
Switch in the stacked group. See the discussion of Switch Stacking below for more
information on stacking GSW-1290/GSW-2492 Switches.
NOTICE: Do not connect the stacked Switch group to the network until
you have properly configured all Switches for stacking. An improperly
configured Switch stack can cause a broadcast storm.
Rear Panel Description
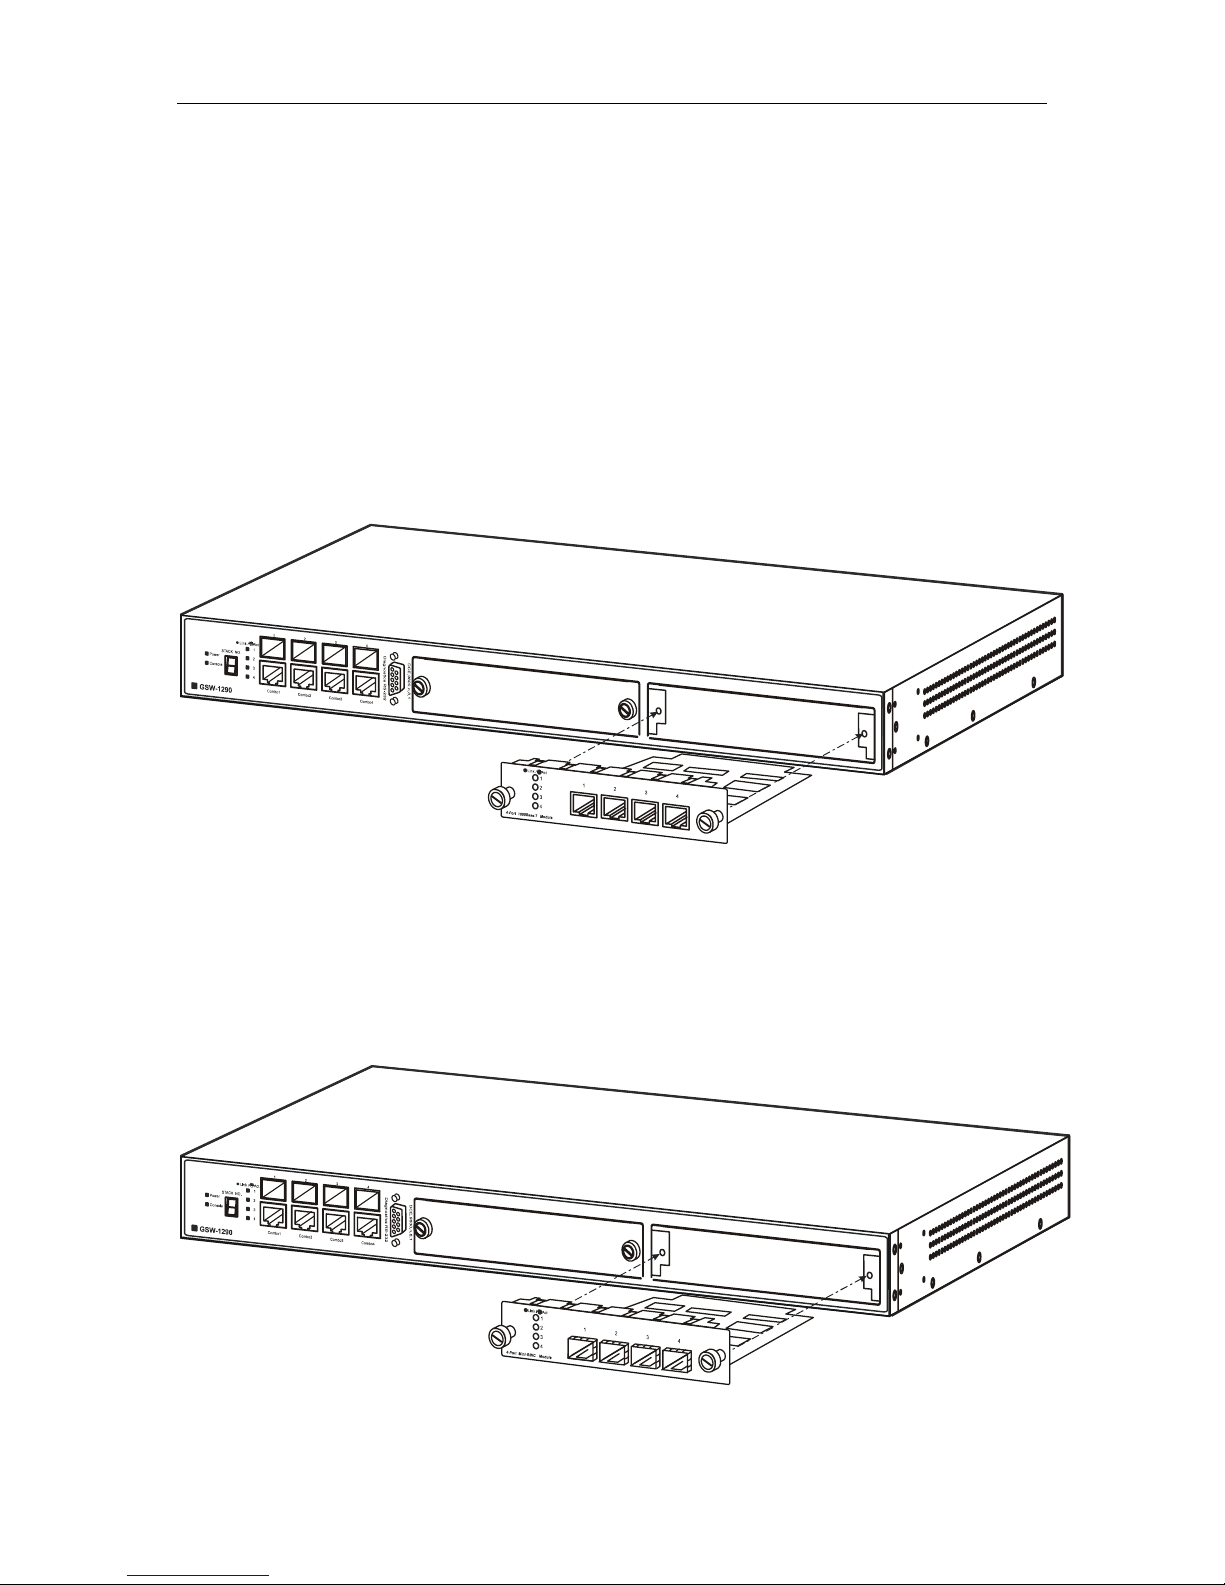
The rear panel of the Switch contains an AC power connector.
14
Page 15
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 1-4. Rear panel view of the Switch
The AC power connector is a standard three-pronged connector that supports the power cord. Plug-in the
female connector of the provided power cord into this socket, and the male side of the cord into a power
outlet. The Switch automatically adjusts its power setting to any supply voltage in the range from 100 ~
240 VAC at 50 ~ 60 Hz.
Plug-in Modules
The GSW-1290 Switch is able to accommodate optional plug-in modules in order to increase functionality
and performance. Two modules may be installed and used in combination with any of the three available
modules. Plug-in modules must be purchased separately.
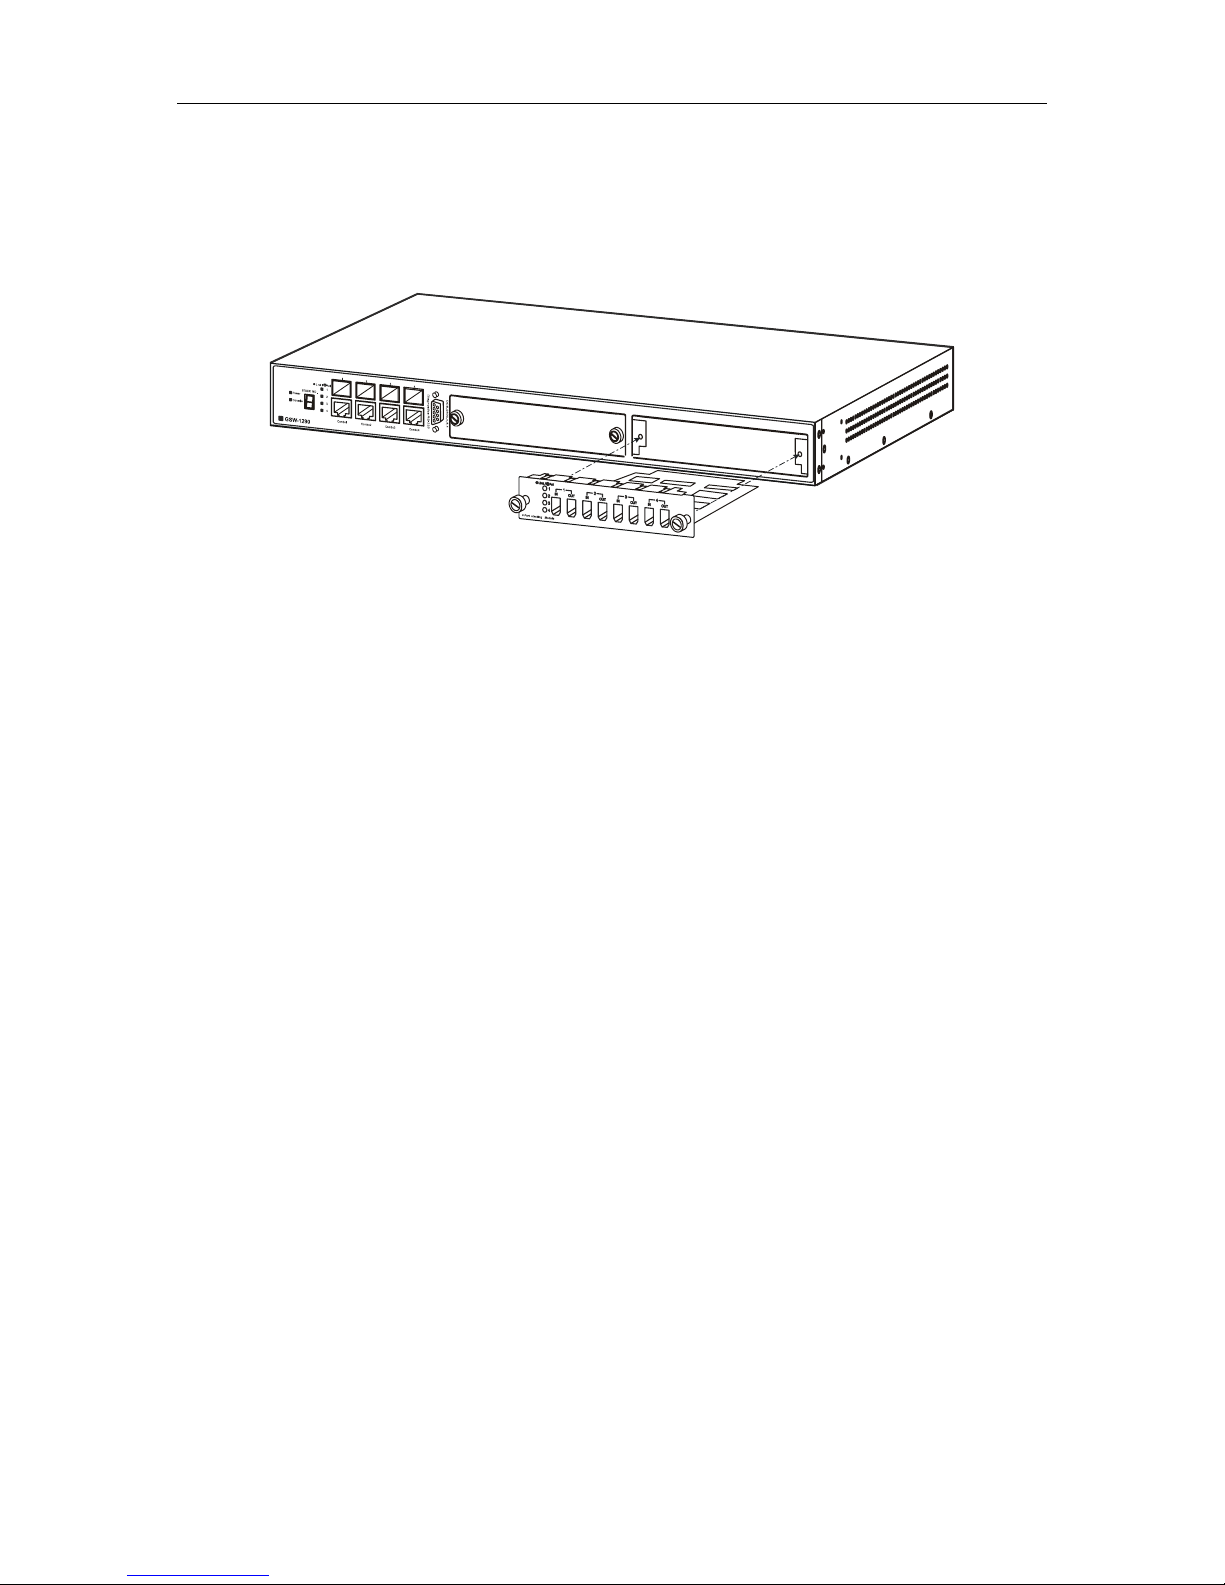
MDU-1290T 1000BASE-T Module
Figure 1-5. 1000BASE-T Four-port module
• Front-panel module
• Connects to 1000BASE-T devices
• LED indicators for Link/Activity
MDU-1290M SFP (Mini GBIC) Module
Figure 1-6. Four-port Gigabit SFP module
15
Page 16
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
• Front-panel module
• Connects to Gigabit Ethernet devices
• LED indicators for Link/Activity and Status
MDU-1290S IEEE 1394 Stacking Module
Figure 1-7. MDU-1290S IEEE 1394 Stacking module
• Front-panel module
• Connect to four GSW-2492 Switches (up to eight additional slave units may be stacked)
• Four transmitting ports and Four receiving port
• Use the connector of IEEE 1394b
• Data rate up to 1000 Mbps
• 8-segment LED display to indicate Switch ID number within the Switch stack
Switch Stacking
The GSW-1290 can be stacked with a GSW-2492, functioning as a Master of the stack. There are two
connection options available to for stacking. One option is to use the built-in combination ports
(1000BASE-T/SFP). The other possibility is to install one or two MDU-1290S stacking modules and
complete the stacking connection through the IEEE 1394 stacking ports. With two stacking modules
installed, the GSW-1290 can be stacked with as many as twelve slave units.
Each optional stacking module allows up to four GSW-2492 Switches to be interconnected in a stack with
the GSW-1290. Two stacking modules may be used to form a nine-Switch stack consisting of one Master
and eight Slaves, managed through the GSW-1290 Master Switch. The stacked group has a single IP
address and is managed as a single device. The entire Switch stack is managed and monitored through the
network or alternatively, through the serial port on the GSW-1290. The stacking modules connect to the
slaves using IEEE 1394 serial cable (Firewire) in a star topology for GSW-2492 groups (see illustration on
page 19).
The stacking ports are marked IN and OUT. The IEEE 1394 compliant cable must be connected from an
IN port on one Switch to an OUT port on the next Switch in the stack.
Restrictions and Cautions for Stacking
The GSW-1290 may serve as the Master of up to twelve additional Switches. The slave Switch units must
meet the following criteria:
All additional slave Switches must be the same model - that is, the slaves must be all GSW-2492 Switches.
The slave unit types cannot be mixed within a single stacked group. Make sure that all Switches in the
group have the latest firmware installed.
16
Page 17
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The GSW-1290 is automatically started as the Master Switch when it is connected in a Switch stack. It is
necessary however to enable stacking for each slave Switch in a stacked group before interconnecting them
and before connecting the group to the network. Stacking can be enabled by connecting to each slave
through the console port and using the CLI stacking configuration command. Before stacking has been
enabled on the slaves, the IEEE 1394 port is treated logically as an individual 1000BASE port in fullduplex mode. Since the Spanning Tree Protocol is disabled by default, a broadcast storm will result if the
stacking link is completed between Switches
that have not been properly configured.
Management Options
The system may be managed out-of-band through the console port on the front panel or in-band using
Telnet, a web browser or SNMP-based management.
NOTE: The CLI stacking command set
for the GSW-1290 is slightly different
from the CLI stacking command set for
the GSW-2492. Please refer to the CLI
Reference Manual for details.
Web-based Management Interface
After you have successfully installed the Switch, you can configure the Switch, monitor the LED panel, and
display statistics graphically using a web browser, such as Opera, Netscape Navigator (version 6.2 and
higher) or Microsoft
® Internet Explorer (version 5.0).
NOTE: To access the Switch through a web browser, the computer
running the web browser must have IP-based network access to the
Switch.
Command Line Console Interface through the Serial Port or Telnet
You can also connect a computer or terminal to the serial console port or use Telnet to access the Switch.
The command-line-driven interface provides complete access to all Switch management features. For a full
list of commands, see the Command Line Reference Manual, which is included on the documentation CD.
SNMP-Based Management
You can manage the Switch with an SNMP-compatible console program. The Switch supports SNMP
version 1.0, version 2.0 and version 3.0. The SNMP agent decodes the incoming SNMP messages and
responds to requests with MIB objects stored in the database. The SNMP agent updates the MIB objects to
generate statistics and counters.
The Switch supports a comprehensive set of MIB extensions:
• RFC 1643 Ether-like MIB
• RFC 1724 RIPv2 MIB
• RFC 1757 RMON
• RFC 1850 OSPF MIB
• RFC 1907 SNMPv2 MIB
• RFC 2021 RMON II MIB
• RFC 2096 IP-FORWARD MIB
• RFC 2233 IF-MIB
• RFC 2358 Ethernet-Link MIB
• RFC 2573 SNMP Notification and Target MIB
• RFC 2574 SNMP User-based SM MIB
• RFC 2575 SNMP View-based ACM MIB
17
Page 18

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
• RFC 2674 802.1p and 802.1q Bridge MIB
• RFC 2737 Entity MIB
• RFC 2932 IPMROUTE STD MIB
• RFC 2933 IGMP MIB
• RFC 2934 PIM MIB
• IEEE8021-PAE 802.1x PAE MIB
18
Page 19
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Chapter 2
Installation
Package Contents
Before You Connect to the Network
Installing the Switch without a Rack
Installing the Switch in a Rack
Connecting Stacked Switch Groups
Configuring a Switch Group for Stacking
External Redundant Power System
Connecting the Console Port
Password Protection
SNMP Settings
IP Address Assignment
Connecting Devices to the Switch
Package Contents
Before you begin installing the Switch, confirm that your package contains the following items:
1. One GSW-1290 Layer 2 Switch
2. Mounting kit: 2 mounting brackets and screws
3. Four rubber feet with adhesive backing
4. One AC power cord
5. This User Manual
6. CLI Reference Manual
Before You Connect to the Network
Before you connect to the network, you must install the Switch on a flat surface or in a rack, set up a
terminal emulation program, plug in the power cord, and then set up a password and IP address.
NOTICE: Do not connect the Switch to the network until you have
established the correct IP settings, user accounts and proper stacking
configuration (if the Switch is stacked).
19
Page 20
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Installing the Switch without the Rack
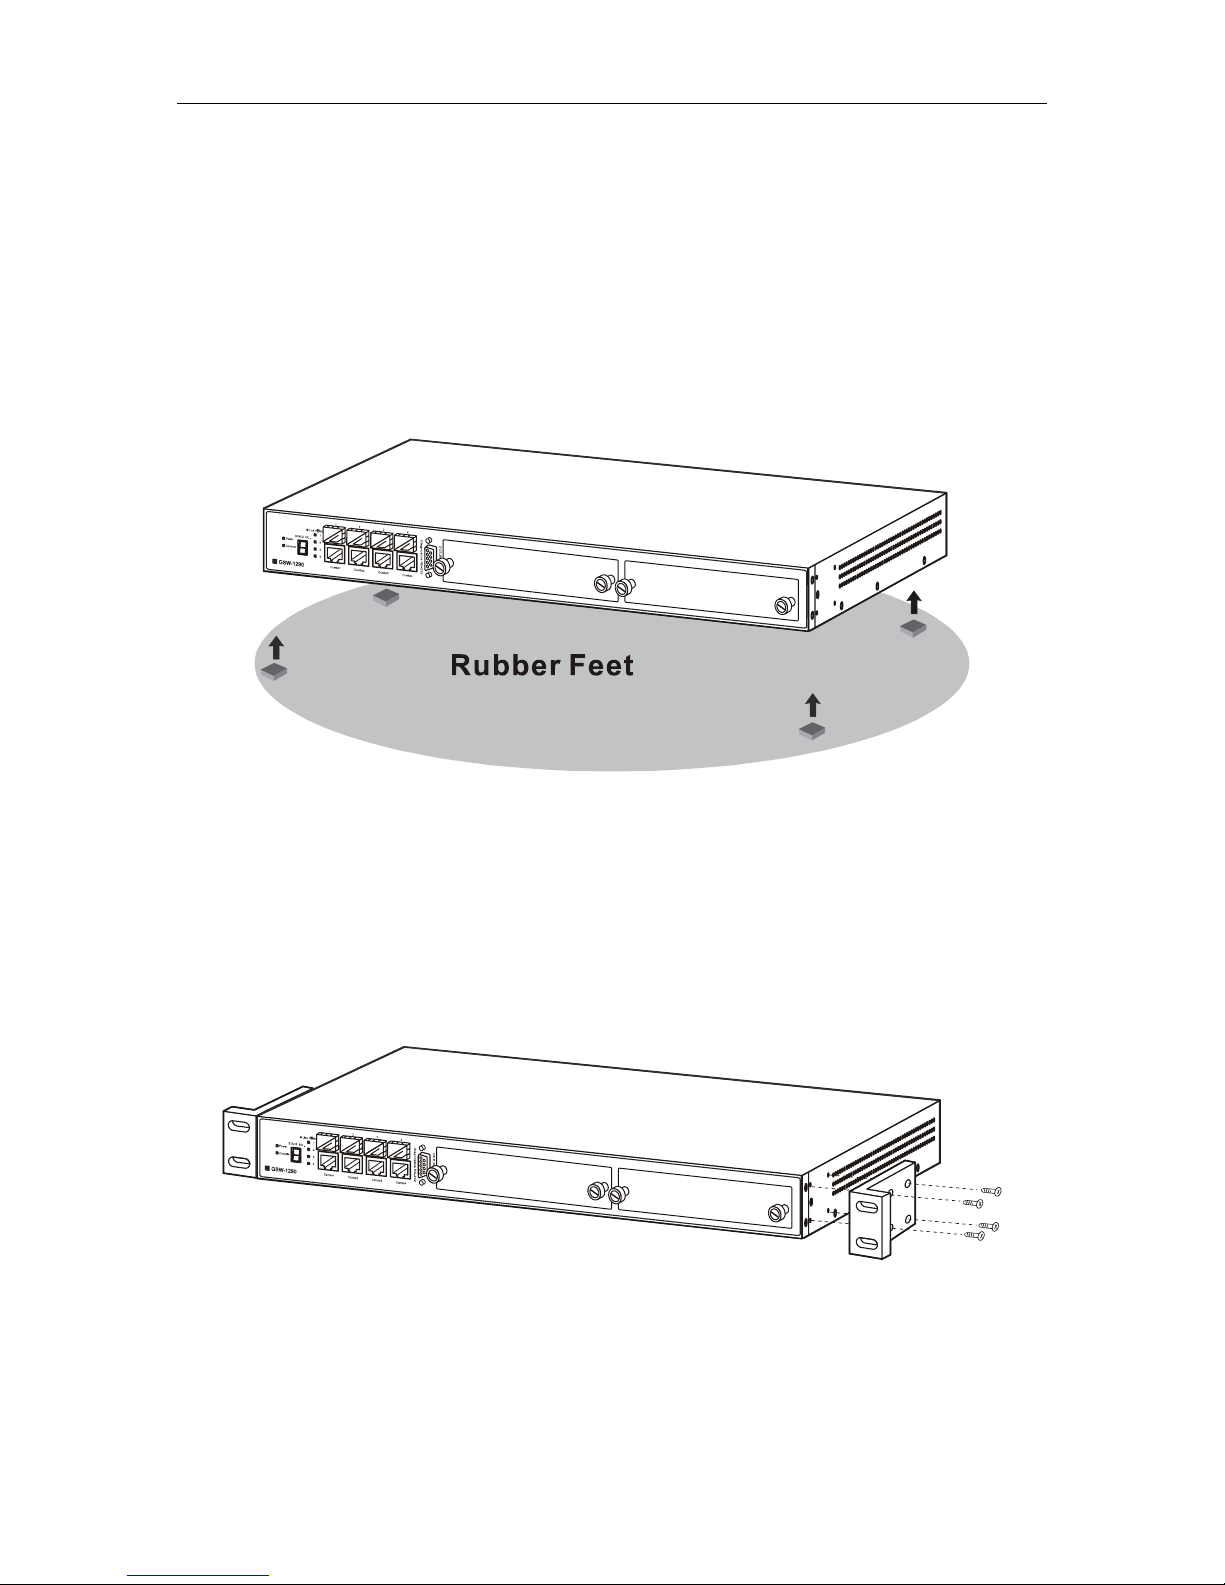
The Switch is supplied with rubber feet for stationing it on a flat surface and mounting brackets and screws
for mounting the Switch in a rack.
Install the Switch on a level surface that can safely support the weight of the Switch and its attached cables.
The Switch must have adequate space for ventilation and for accessing cable connectors.
Set the Switch on a flat surface and check for proper ventilation. Allow at least 5 cm (2 inches) on each
side of the Switch and 15 cm (6 inches) at the back for the power cable.
Attach the rubber feet on the marked locations on the bottom of the chassis.
The rubber feet, although optional, are recommended to keep the unit from slipping.
Figure 2-1. Install rubber feet for installations with or without a rack
Installing the Switch in a Rack
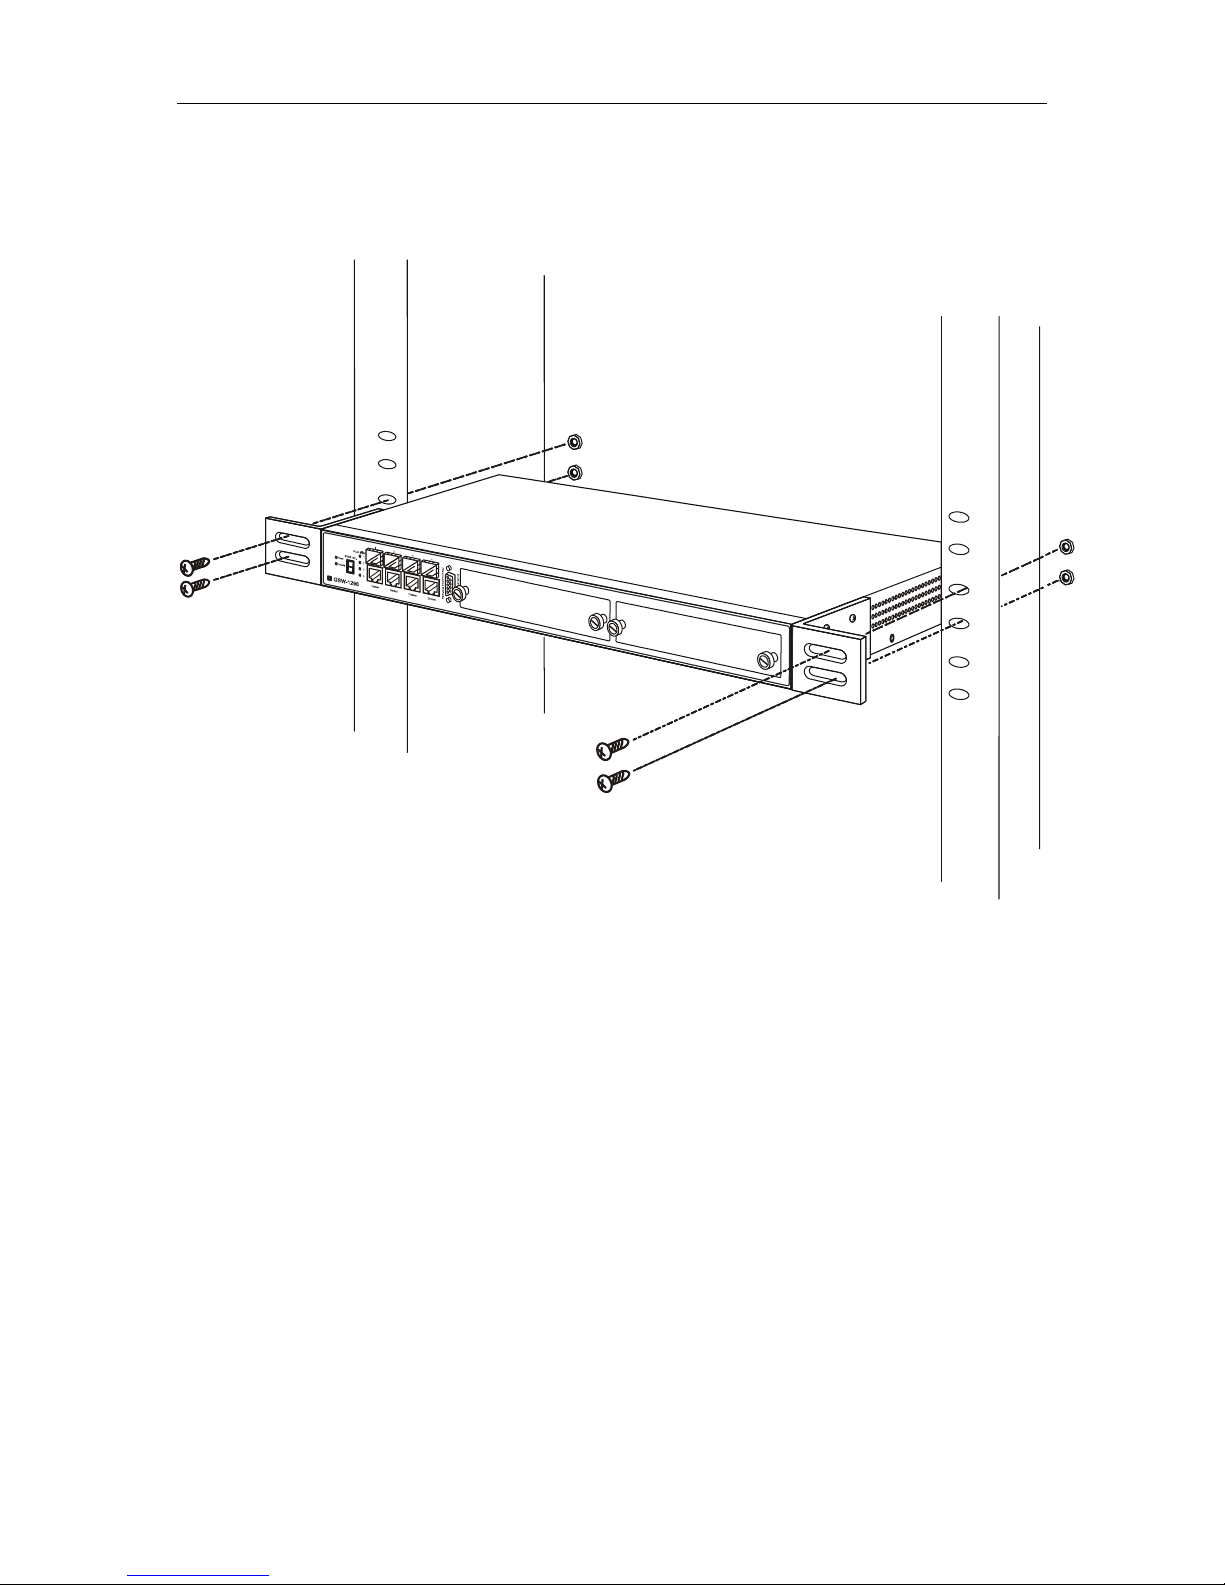
You can install the Switch in most standard 19-inch (48.3-cm) racks. Refer to the illustrations below.
Use the supplied screws to attach a mounting bracket to each side of the Switch.
Align the holes in the mounting bracket with the holes in the rack.
Insert and tighten two screws through each of the mounting brackets.
Figure 2-2. Attach mounting brackets
20
Page 21
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 2-3. Install Switch in equipment rack
21
Page 22
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
22
Page 23
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Connecting Stacked Switch Groups
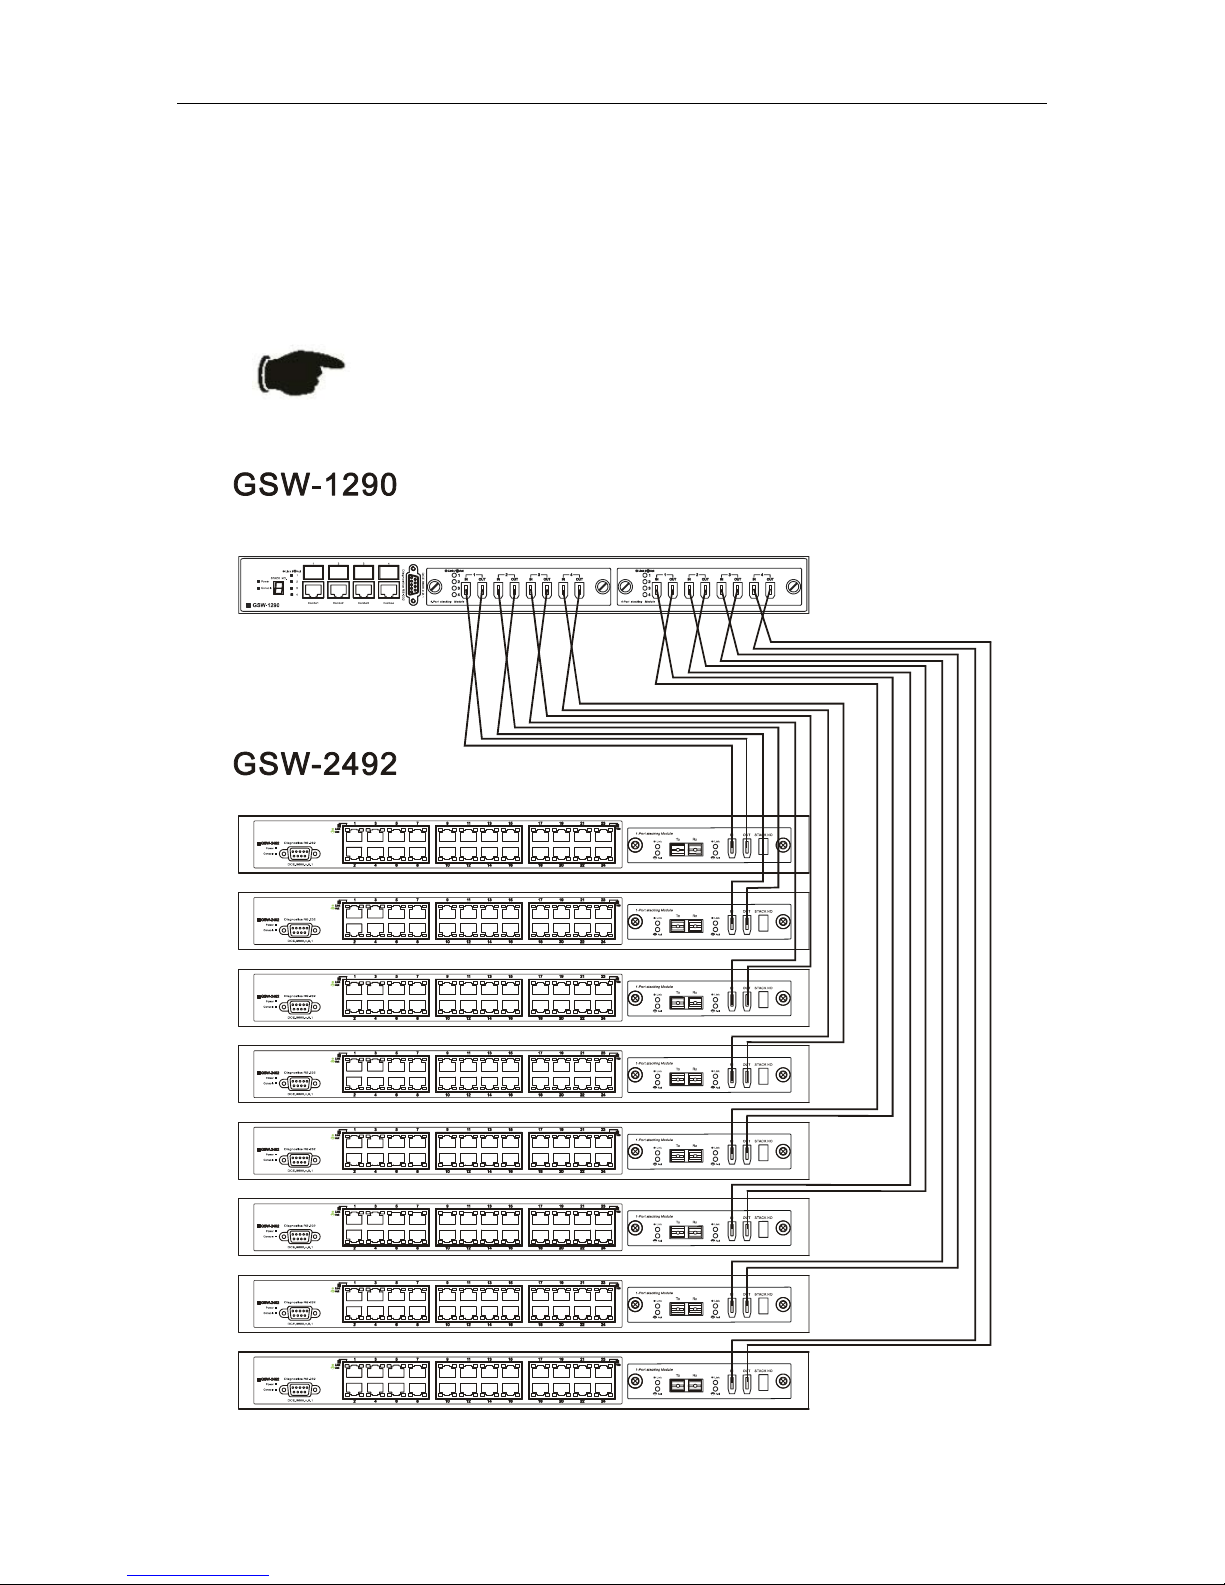
The GSW-1290 may be configured to function as the Master of a stacked group of GSW-2492 Switches
(see Restrictions for Stacking on page 16). A stacked group of GSW-2492 Switches connects to the GSW1290 in a star topology. The instructions below, tell you how to configure the GSW-1290 to function as a
Master, as well as how to configure the GSW-2492 to function as a slave Switch units using the CLI
interface.
NOTICE: Do not connect the stacked Switch group to the network until
you have properly configured all Switches for stacking. An improperly
configured Switch stack can cause a broadcast storm.
23
Page 24
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 2-4. Star topology stacked Switch group connected via IEEE 1394 cabling
The stacking ports are marked IN and OUT. The IEEE 1394 compliant cable must be connected from an
IN port on one Switch to an OUT port on the next Switch in the stack.
24
Page 25
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Configuring a Switch Group for Stacking
Follow the instructions below to first configure the slave units, and then to configure the GSW-1290 as the
designated Master.
For the GSW-2492 the stacking configuration as a Master or Slave Switch is no longer necessary. The
GSW-1290 can communicate with a GSW-2492 regardless of its stacking configuration. It is recommended
that you configure all GSW-2492 Switches in a Switch stack in the auto stacking mode to reduce the
potential for problems. The default stacking mode configuration for the GSW-2492 is auto.
To configure the GSW-2492 to function in a stacked group as a slave, do the following:
At the CLI login prompt, enter config stacking mode enable auto and press the Enter key.
You will be prompted to save the stacking mode configuration. Press the Y key (yes) to save the stacking
mode configuration.
Successful configuration will be verified by a Success message. It takes a few seconds for the change to
take effect and be saved. See the example below for the GSW-2492.
NOTICE: The GSW-1290 can be used to manage a Switch stack
consisting of only GSW-2492 Switches.
GSW-2492:4#config stacking mode enable auto
Command: config stacking mode enable auto
Do you want to save the new system configuration to NV-RAM now?(y/n)
Saving all configurations to NV-RAM... Done.
Success.
GSW-2492:4#............
The default settings for the GSW-1290 has the stacking mode enabled. However if the stacking mode has
been disabled it will be necessary to enable it. Follow the instructions below to change the stacking mode to
enable. If you do not know what the stacking mode setting currently is, use the command show
stacking mode.
To enable stacking in the GSW-1290, do the following:
At the CLI login prompt, enter config stacking mode enable and press the Enter key.
You will be prompted to save the stacking mode configuration. If you save the new stacking mode by
pressing the Y key, the settings will be saved and the Switch will restart.
Press the Y key (yes) to save the stacking mode configuration and restart the switch.
25
Page 26
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
GSW-1290:4#config stacking mode enable
Command: config stacking mode enable
The new stacking mode configuration must be saved and the system restarted
to put the new settings into effect.
If you do not save the changes now, they will be lost.
Saving all configurations to NV-RAM... 15%
Changing the stacking mode in the GSW-1290 will automatically save the settings and restart the system. It
will take a few minutes to complete the process.
Unit ID Display for Switches in a Switch Stack
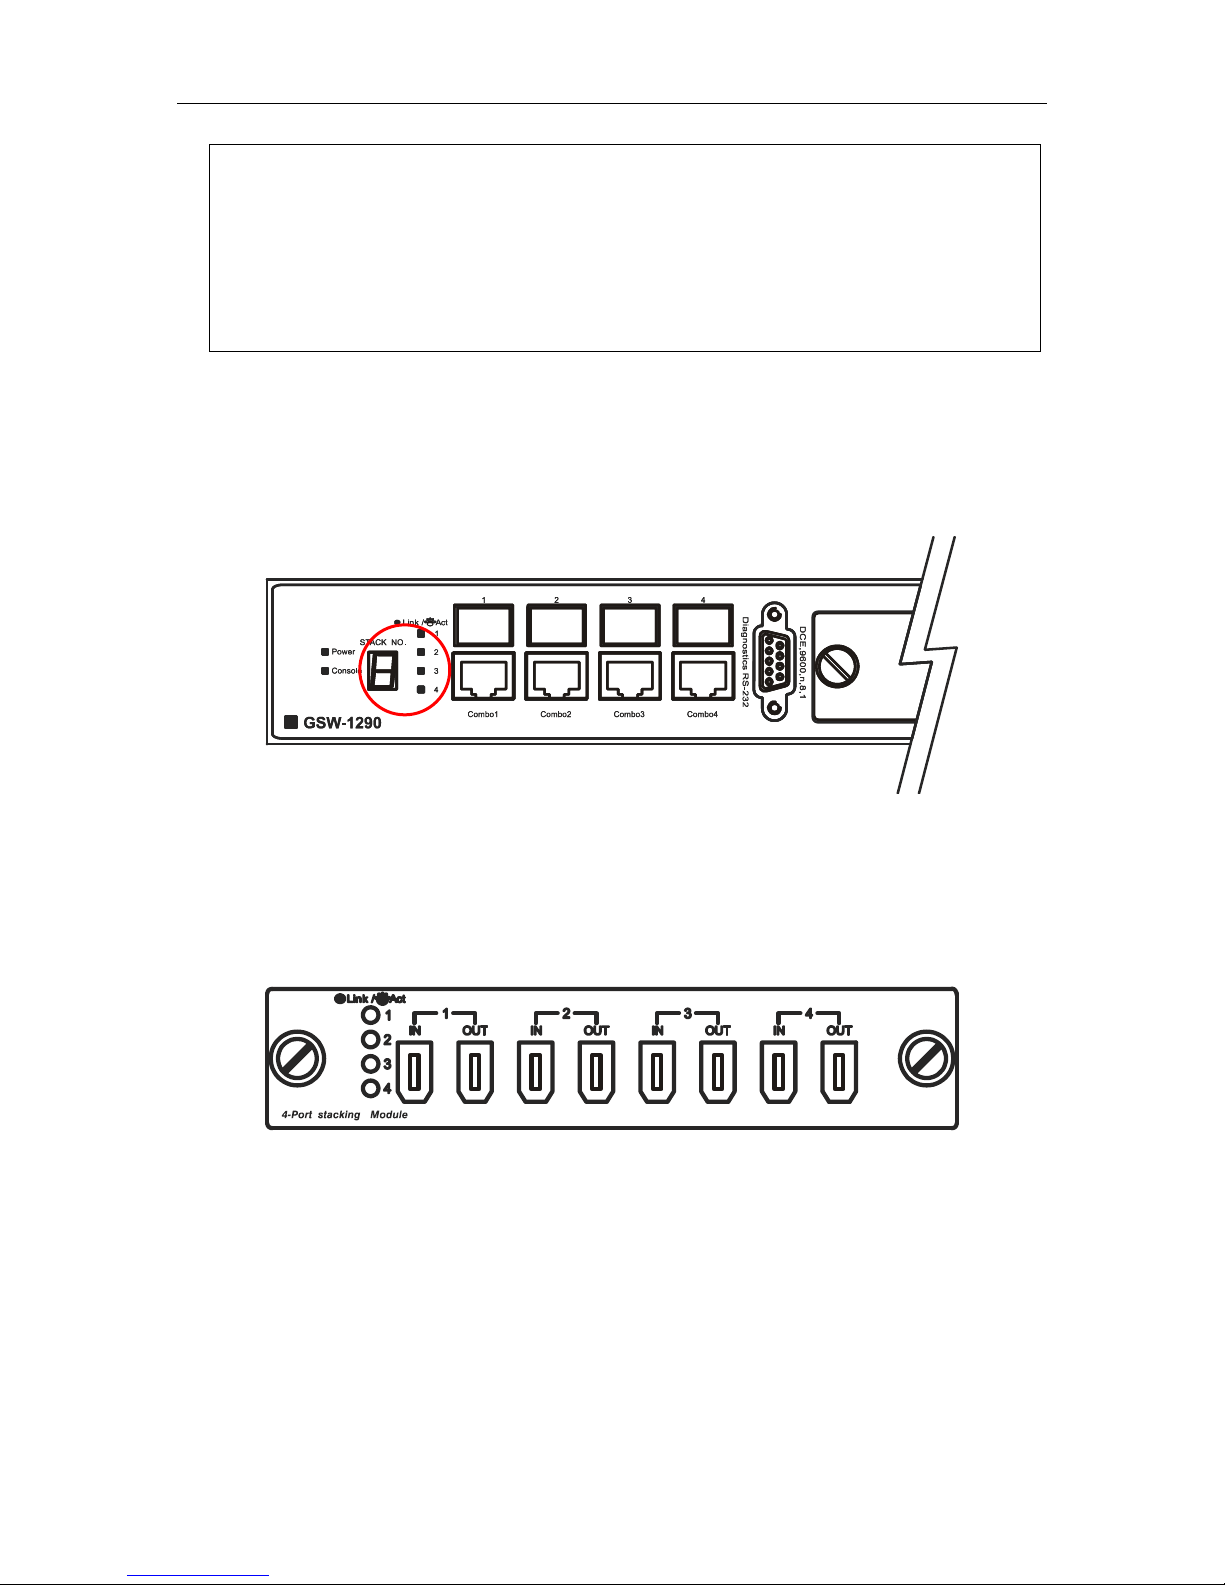
The Stack ID 7-segment LED (as shown below) on the front panel of the GSW-1290 will always display F
(15 in hex). An F will also be displayed in the Stack ID LED even if the GSW-1290 is in standalone mode.
Figure 2-5. GSW-1290 Front Panel (left side)
The Unit ID of individual GSW-2492 Switches in a Switch stack is determined by the port number of the
port on the GSW-1290 that the Switch is connected to. The ports on the GSW-1290 are numbered starting
with port 1 from left to right along the front panel of the Switch. For example, the four combination ports
next to the Stack NO. LED are numbered 1 through 4, so if a four port stacking module is installed in the
first module slot, the stacking ports will be numbered 5 through 8. If two stacking modules are installed in
the GSW-1290, then the stacking ports on the second module will be numbered 9 through 12.
Figure 2-6. MDU-1290S Stacking Module Front Panel
If the a stacking module is installed in the GSW-1290’s first module slot, then the first IN/OUT pair in the
figure above will be port 5. If a GSW-2492 in a Switch stack is connected to the first stacking port (port
number 5 on the GSW-1290), then the Unit ID of the GSW-2492 will be 5.
The Unit ID of the GSW-2492 will be displayed in the STACK NO. LED on the front panel of the GSW2492’s stacking module, as shown below.
26
Page 27

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 2-7. MDU-2492S Stacking Module Front Panel
27
Page 28
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Connecting the Console Port
The Switch provides an RS-232 serial port that enables a connection to a computer or terminal for
monitoring and configuring the Switch. This port is a male DB-9 connector, implemented as a data terminal
equipment (DTE) connection.
To use the console port, you need the following equipment:
• A terminal or a computer with both a serial port and the ability to emulate a terminal
• A null modem or crossover RS-232 cable with a female DB-9 connector for the console port on
the Switch
• To connect a terminal to the console port:
• Connect the female connector of the RS-232 cable directly to the console port on the Switch, and
tighten the captive retaining screws.
• Connect the other end of the cable to a terminal or to the serial connector of a computer running
terminal emulation software. Set the terminal emulation software as follows:
• Select the appropriate serial port (COM port 1 or COM port 2).
• Set the data rate to 9600 baud.
• Set the data format to 8 data bits, 1 stop bit, and no parity.
• Set flow control to
• Under Properties, select VT100 for Emulation mode.
• Select Terminal keys for Function, Arrow, and Ctrl keys. Ensure that you select Terminal keys
(not Windows keys).
NOTICE: When you use HyperTerminal with the Microsoft® Windows® 2000 operating
system, ensure that you have Windows 2000 Service Pack 2 or later installed.
Windows 2000 Service Pack 2 allows you to use arrow keys in HyperTerminal’s VT100
emulation. See www.microsoft.com for information on Windows 2000 service packs.
none.
After you have correctly set up the terminal, plug the power cable into the power receptacle on the back of
the Switch. The boot sequence appears in the terminal.
After the boot sequence completes, the console login screen displays.
If you have not logged into the command line interface (CLI) program, press the Enter key at the User
name and password prompts. There is no default user name and password for the Switch, user names and
passwords must first be created by the administrator. If you have previously set up user accounts, log in and
continue to configure the Switch.
Enter the commands to complete your desired tasks. Many commands require administrator-level access
privileges. Read the next section for more information on setting up user accounts. See the Command Line
Reference on the documentation CD for a list of all commands and additional information on using the CLI.
When you have completed your tasks, exit the session with the logout command or close the emulator
program.
Password Protection
The GSW-1290 does not have a default user name and password. One of the first tasks when settings up the
Switch is to create user accounts. If you log in using a predefined administrator-level user name you have
privileged access to the Switch’s management software.
After your initial login, define new passwords for both default user names to prevent unauthorized access to
the Switch, and record the passwords for future reference.
28
Page 29
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
To create an administrator-level account for the Switch, do the following:
At the CLI login prompt, enter create account admin followed by the <user name> and press the Enter
key.
You will be asked to provide a password. Type the <password>
used for the administrator account being created and press the
Enter key.
NOTE: Passwords
are case sensitive.
You will be prompted to enter the same password again to
verify it. Type the same password and press the Enter key.
Successful creation of the new administrator account will be verified by a Success message.
User names and passwords can be up to 15 characters in length.
The sample below illustrates a successful creation of a new administrator-level account with the user name
“newmanager”.
GSW-1290:4#create account admin newmanager
Command: create account admin newmanager
Enter a case-sensitive new password:********
Enter the new password again for confirmation:********
Success.
GSW-1290:4#
NOTICE: CLI configuration commands only modify the running configuration file
and are not saved when the Switch is rebooted. To save all your configuration
changes in nonvolatile storage, you must use the save command to copy the
running configuration file to the startup configuration.
SNMP Settings
Simple Network Management Protocol (SNMP) is an OSI Layer 7 (Application Layer) designed
specifically for managing and monitoring network devices. SNMP enables network management stations to
read and modify the settings of gateways, routers, Switches, and other network devices. Use SNMP to
configure system features for proper operation, monitor performance and detect potential problems in the
Switch, Switch group or network.
Managed devices that support SNMP include software (referred to as an agent), which runs locally on the
device. A defined set of variables (managed objects) is maintained by the SNMP agent and used to manage
the device. These objects are defined in a Management Information Base (MIB), which provides a standard
presentation of the information controlled by the on-board SNMP agent. SNMP defines both the format of
the MIB specifications and the protocol used to access this information over the network.
The GSW-1290 supports the SNMP versions 1, 2c, and 3. You can specify which version of the SNMP you
want to use to monitor and control the Switch. The three versions of SNMP vary in the level of security
provided between the management station and the network device.
29
Page 30

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
In SNMP v.1 and v.2, user authentication is accomplished using ‘community strings’, which function like
passwords. The remote user SNMP application and the Switch SNMP must use the same community string.
SNMP packets from any station that has not been authenticated are ignored (dropped).
The default community strings for the Switch used for SNMP v.1 and v.2 management access are:
public - Allows authorized management stations to retrieve MIB objects.
private - Allows authorized management stations to retrieve and modify MIB objects.
SNMP v.3 uses a more sophisticated authentication process that is separated into two parts. The first part is
to maintain a list of users and their attributes that are allowed to act as SNMP managers. The second part
describes what each user on that list can do as an SNMP manager.
The Switch allows groups of users to be listed and configured with a shared set of privileges. The SNMP
version may also be set for a listed group of SNMP managers. Thus, you may create a group of SNMP
managers that are allowed to view read-only information or receive traps using SNMP v.1 while assigning
a higher level of security to another group, granting read/write privileges using SNMP v.3.
Using SNMP v.3 individual users or groups of SNMP managers can be allowed to perform or be restricted
from performing specific SNMP management functions. The functions allowed or restricted are defined
using the Object Identifier (OID) associated with a specific MIB. An additional layer of security is
available for SNMP v.3 in that SNMP messages may be encrypted. To read more about how to configure
SNMP v.3 settings for the Switch read the next section, Management.
Traps
Traps are messages that alert network personnel of events that occur on the Switch. The events can be as
serious as a reboot (someone accidentally turned OFF the Switch), or less serious like a port status change.
The Switch generates traps and sends them to the trap recipient (or network manager). Typical traps include
trap messages for Authentication Failure, Topology Change and Broadcast\Multicast Storm.
MIBs
Management and counter information are stored by the Switch in the Management Information Base (MIB).
The Switch uses the standard MIB-II Management Information Base module. Consequently, values for
MIB objects can be retrieved from any SNMP-based network management software. In addition to the
standard MIB-II, the Switch also supports its own proprietary enterprise MIB as an extended Management
Information Base. The proprietary MIB may also be retrieved by specifying the MIB Object Identifier.
MIB values can be either read-only or read-write.
IP Address Assignment
Each Switch must be assigned its own IP Address, which is used for communication with an SNMP
network manager or other TCP/IP application (for example BOOTP, TFTP). The Switch’s default IP
address is 10.90.90.90. You can change the default Switch IP address to meet the specification of your
networking address scheme.
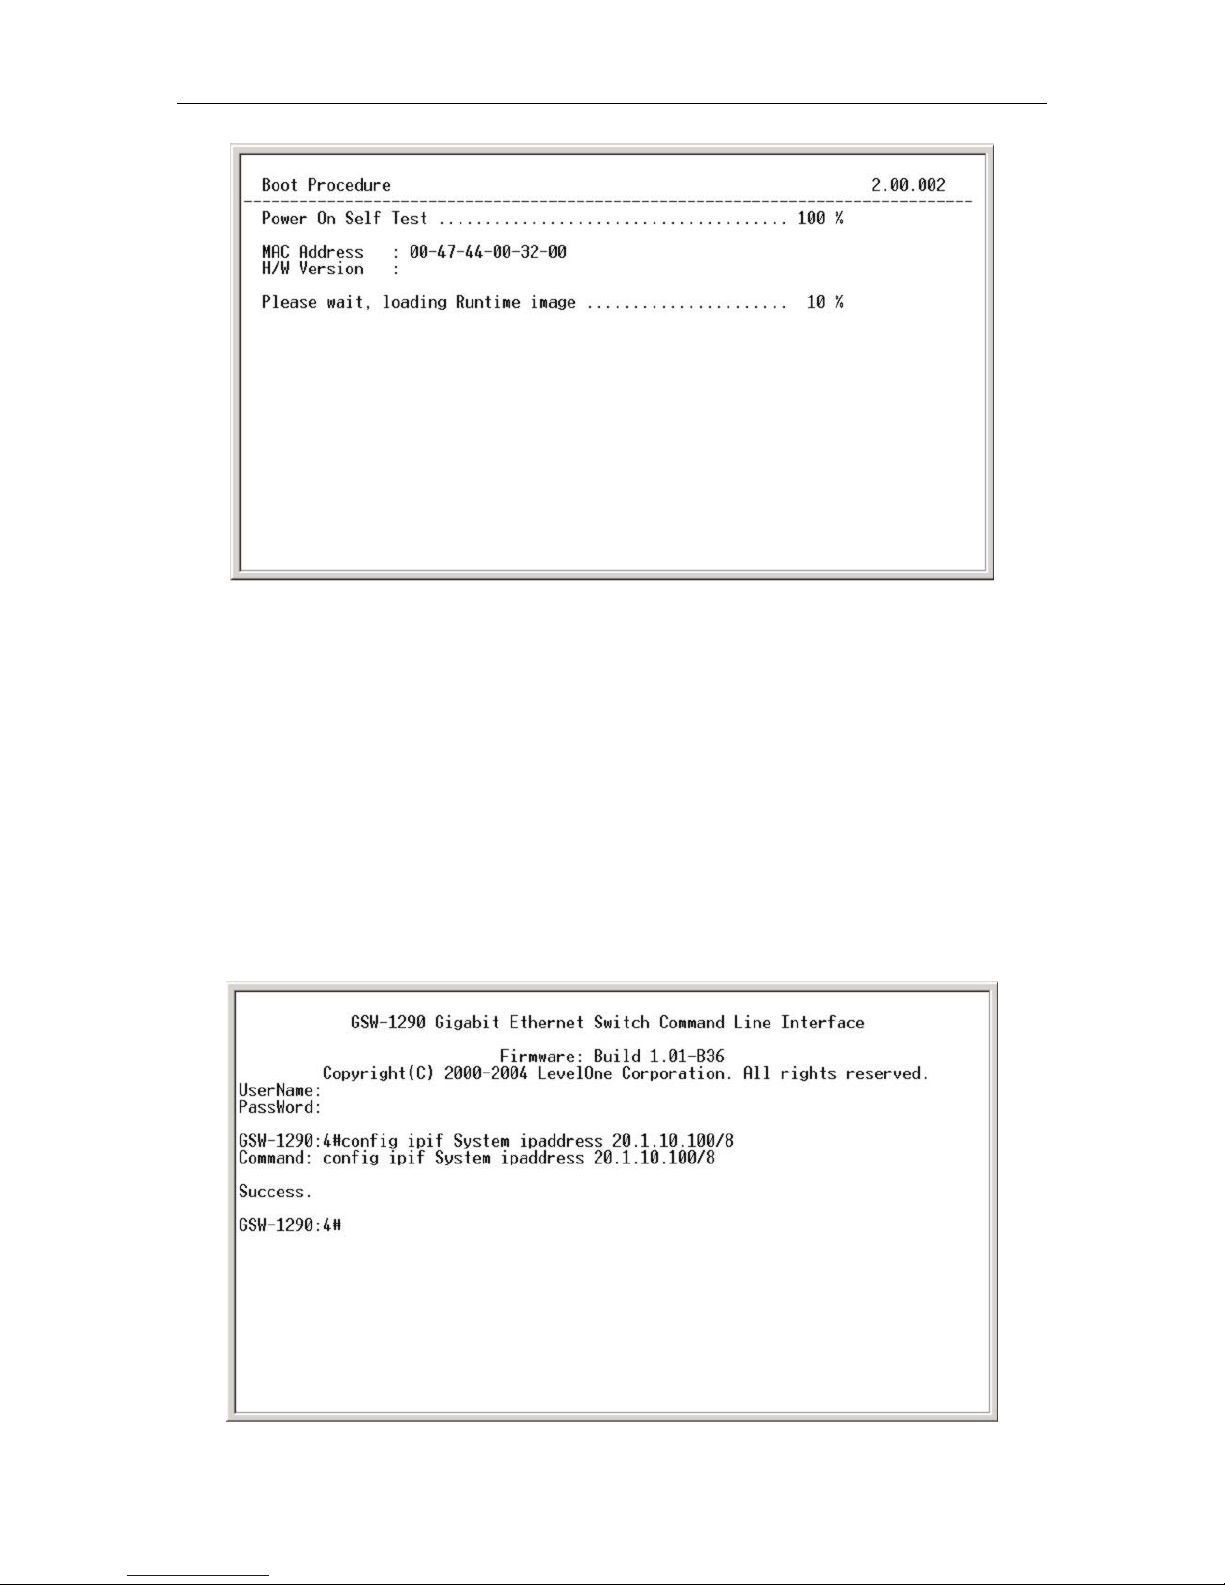
The Switch is also assigned a unique MAC address by the factory. This MAC address cannot be changed,
and can be found from the initial boot console screen – shown below.
30
Page 31
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 2-8. Boot screen
The Switch’s MAC address can also be found from the Web management program on the Switch
Information (Basic Settings) window on the Configuration menu.
The IP address for the Switch must be set before it can be managed with the Web-based manager. The
Switch IP address can be automatically set using BOOTP or DHCP protocols, in which case the actual
address assigned to the Switch must be known.
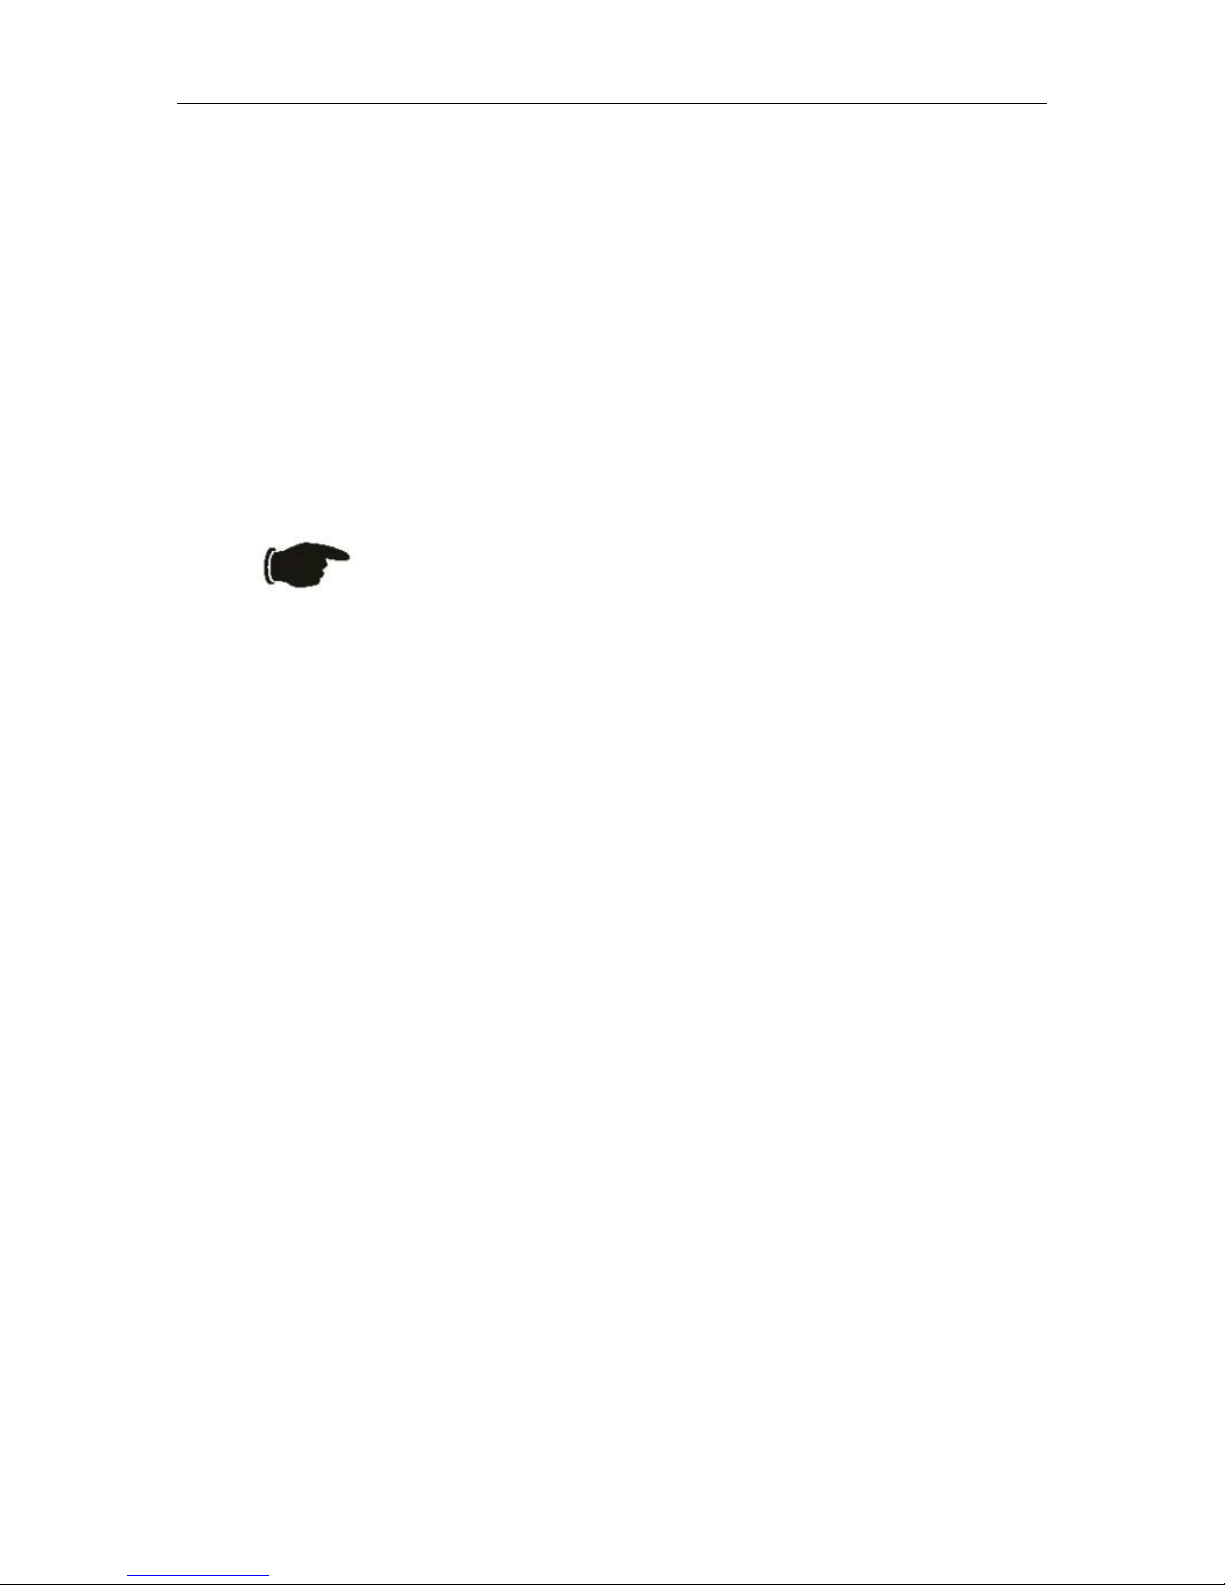
The IP address may be set using the Command Line Interface (CLI) over the console serial port as follows:
Starting at the command line prompt, enter the commands config ipif System ipaddress
xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy. Where the x’s represent the IP address to be assigned to the IP interface
named System and the y’s represent the corresponding subnet mask.
Alternatively, you can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x’s represent the
IP address to be assigned to the IP interface named System and the z represents the corresponding number
of subnets in CIDR notation.
The IP interface named System on the Switch can be assigned an IP address and subnet mask that can then
be used to connect a management station to the Switch’s Telnet or Web-based management agent.
31
Page 32
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 2-9. Assigning the Switch an IP Address
In the above example, the Switch was assigned an IP address of 20.1.10.100 with a subnet mask of
255.0.0.0. The system message Success indicates that the command was executed successfully. The Switch
can now be configured and managed via Telnet and the CLI or via the Web-based management.
Connecting Devices to the Switch
After you assign IP addresses to the Switch, you can connect devices to the Switch.
To connect a device to an SFP transceiver port:
Use your cabling requirements to select an appropriate SFP transceiver type.
Insert the SFP transceiver (sold separately) into the SFP transceiver slot.
Use the appropriate network cabling to connect a device to the connectors on the SFP transceiver.
NOTICE: When the SFP transceiver acquires a link, the associated
integrated 10/100/1000BASE-T port is disabled.
32
Page 33
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Chapter 3
Basic Switch Management
Before You Start
Web-based User Interface
Basic Setup
Switch Information
Switch IP Settings
Security IP Management Stations
User Accounts Management
Saving Changes
Factory Reset
Restart System
Advanced Settings
Switch Stack Management
All software function of the GSW-1290 can managed, configured and monitored via the embedded webbased (HTML) interface. The Switch can be managed from remote stations anywhere on the network
through a standard browser such as Opera, Netscape Navigator/Communicator or Microsoft Internet
Explorer. The browser acts as a universal access tool and can communicate directly with the Switch using
the HTTP protocol.
The web-based management module and the Console program (and Telnet) are different ways to access the
same internal Switching software and configure it. Thus, all settings encountered in web-based
management are the same as those found in the console program.
Before You Start
The GSW-1290 Layer 2 Switch supports a wide array of functions and gives great flexibility and increased
network performance.
This flexibility and rich feature set requires a bit of thought to create a deployment strategy that will
maximize the potential of the GSW-1290 Layer 2 Switch. Please read the portions of this manual pertaining
to the functions you wish to perform with the Switch.
33
Page 34
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Web-based User Interface
The user interface provides access to various Switch configuration and management windows, allows you
to view performance statistics, and permits you to graphically monitor the system status.
Areas of the User Interface
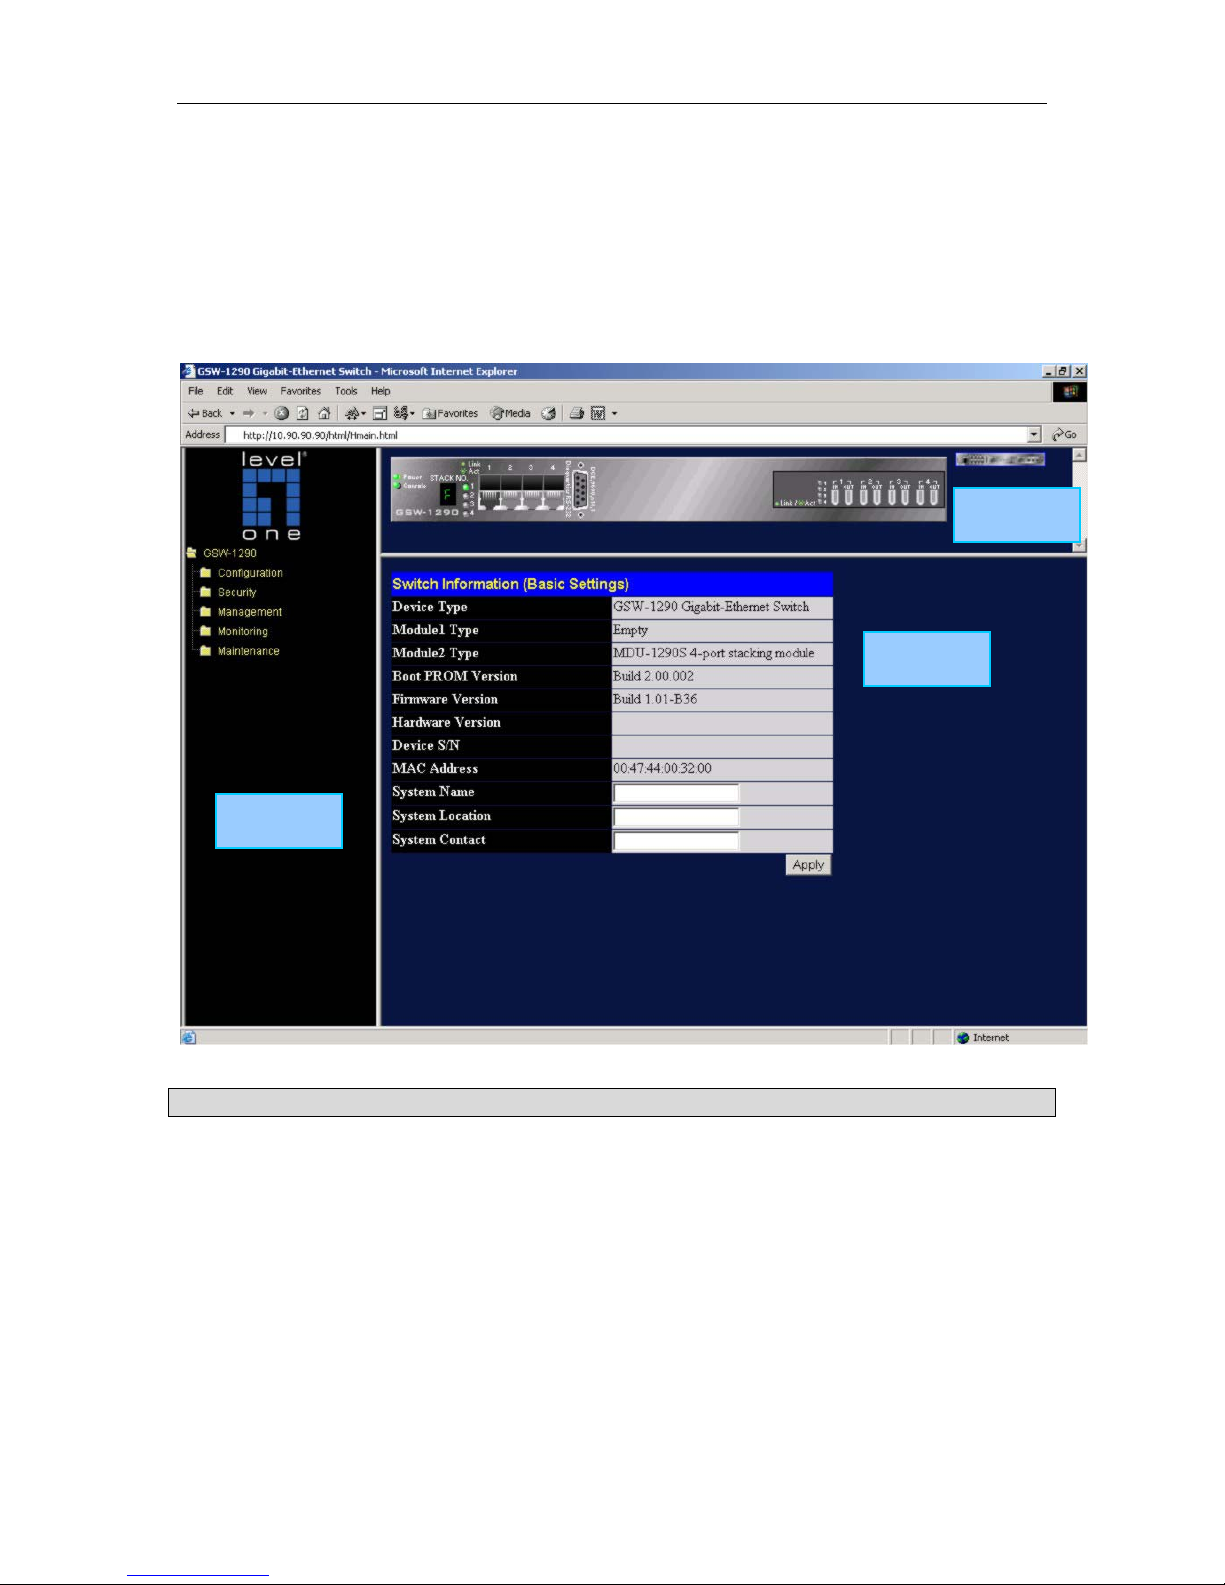
The figure below shows the user interface. The user interface is divided into three distinct areas as
described in the table below.
Area 1
Area 3
Area 2
Area Function
Presents a graphical near real-time image of the front panel of the Switch. This
area displays the Switch’s ports and expansion modules. When the Switch is
1
2
3
stacked a virtual representation of the Switch stack appears in the right hand
portion.
Click on the ports in the front panel to manage the port’s configuration or view
data for the port.
Select the window to be displayed. The folder icons can be opened to display the
hyperlinked window buttons and sub-folders contained within them.
Presents the information selected for configuration or display.
Figure 3-1. Main Web-Manager window
34
Page 35

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Login to Web Manager
To begin managing the Switch simply run the browser you have installed on your computer and point it to
the IP address you have defined for the device. The URL in the address bar should read something like:
http://123.123.123.123, where the numbers 123 represent the IP address of the Switch.
NOTE: The Factory default IP address for the Switch is 10.90.90.90.
In the Welcome page, click on the Login hyperlink; this opens a login dialog box. Enter a user name and
password to access the Switch’s management main page (pictured above). There is no user name or
password configured for the Switch in the default settings, so if this is the first time logging in it is not
necessary to enter these.
NOTICE: Any changes made to the Switch configuration during the current
session must be saved in the Save Configuration window (explained
below) or use the command line interface (CLI) command save.
Web Pages and Folders
Below is a list and description of the main folders and windows available in the web interface:
Configuration: This folder includes all the sub-folders and windows used to configure various
performance functions of the Switch.
Security: This folder contains the Port Access Entity (PAE) sub-folder used to configure 802.1x and
RADIUS server settings. The Trusted Host window link is located here as well.
Management: The windows used to configure SNMP settings, management IP stations, and user accounts
are located here.
Monitoring: Data tables for performance statistics, application and protocol status are contained in the
links and subfolders of this folder.
Maintenance: Contains windows for upgrading firmware and saving configuration files (TFTP Services),
saving configuration changes, resetting and rebooting the Switch, PING test, and logging out of the web
manager.
Single IP Management: SIM settings, Topology, Firmware Update, and Configuration Backup/Restore
windows are located here.
NOTE: Be sure to configure the user name and password in the User
Accounts window before connecting the Switch to the greater network.
35
Page 36
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Switch Information
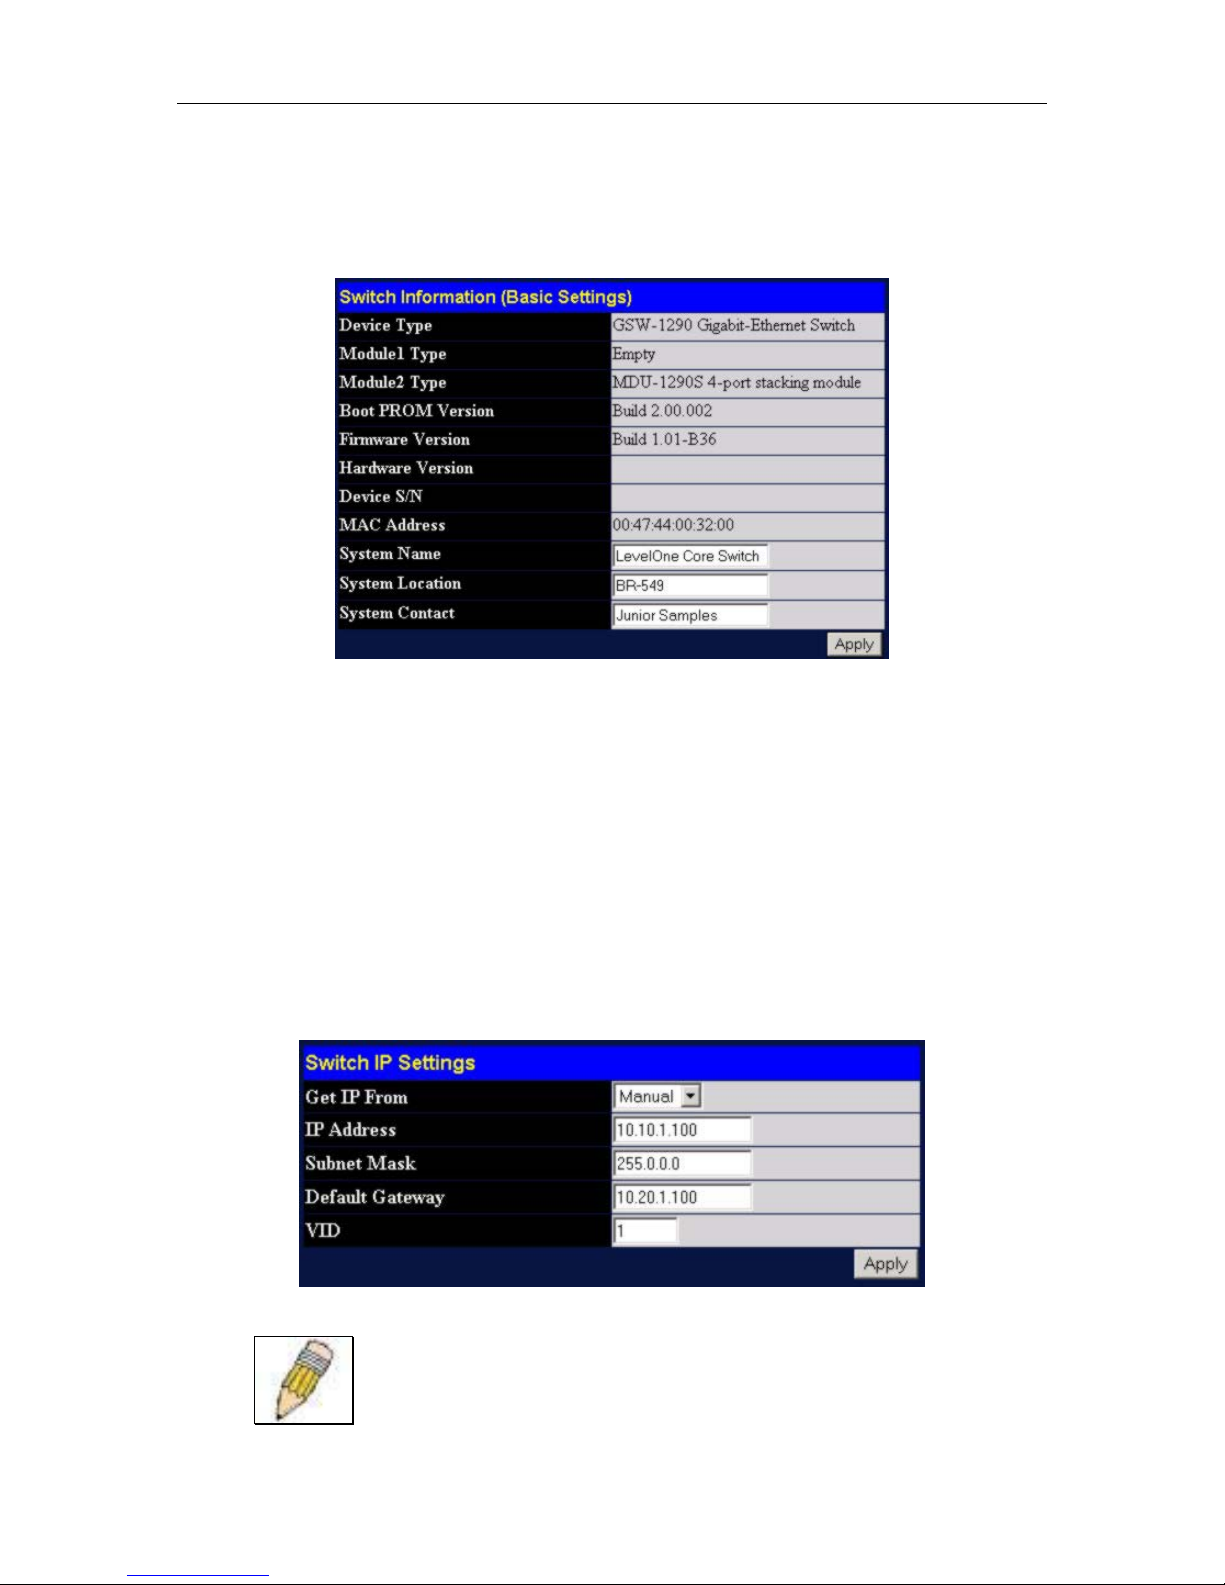
The first page displayed upon logging in is the System Information (Basic Settings) window. This
window can be accessed at any time by clicking the Switch Information button in the Configuration
folder.
Figure 3-2. Switch Information (Basic Settings) menu
This window displays general information about the Switch including its MAC Address, Hardware Boot
PROM version and Firmware version, as well as installed module information.
Switch IP Settings
Switch IP settings may initially be set using the console interface prior to connecting to it through the
Ethernet. If the Switch IP address has not yet been changed, read the Introduction of the CLI Reference or
skip ahead to the end of this section for a quick description of how to use the console port and CLI IP
settings commands to establish IP settings for the Switch.
To change IP settings using the web manager you must access the Switch IP Settings window located in
the Configuration folder.
To configure the Switch’s IP address:
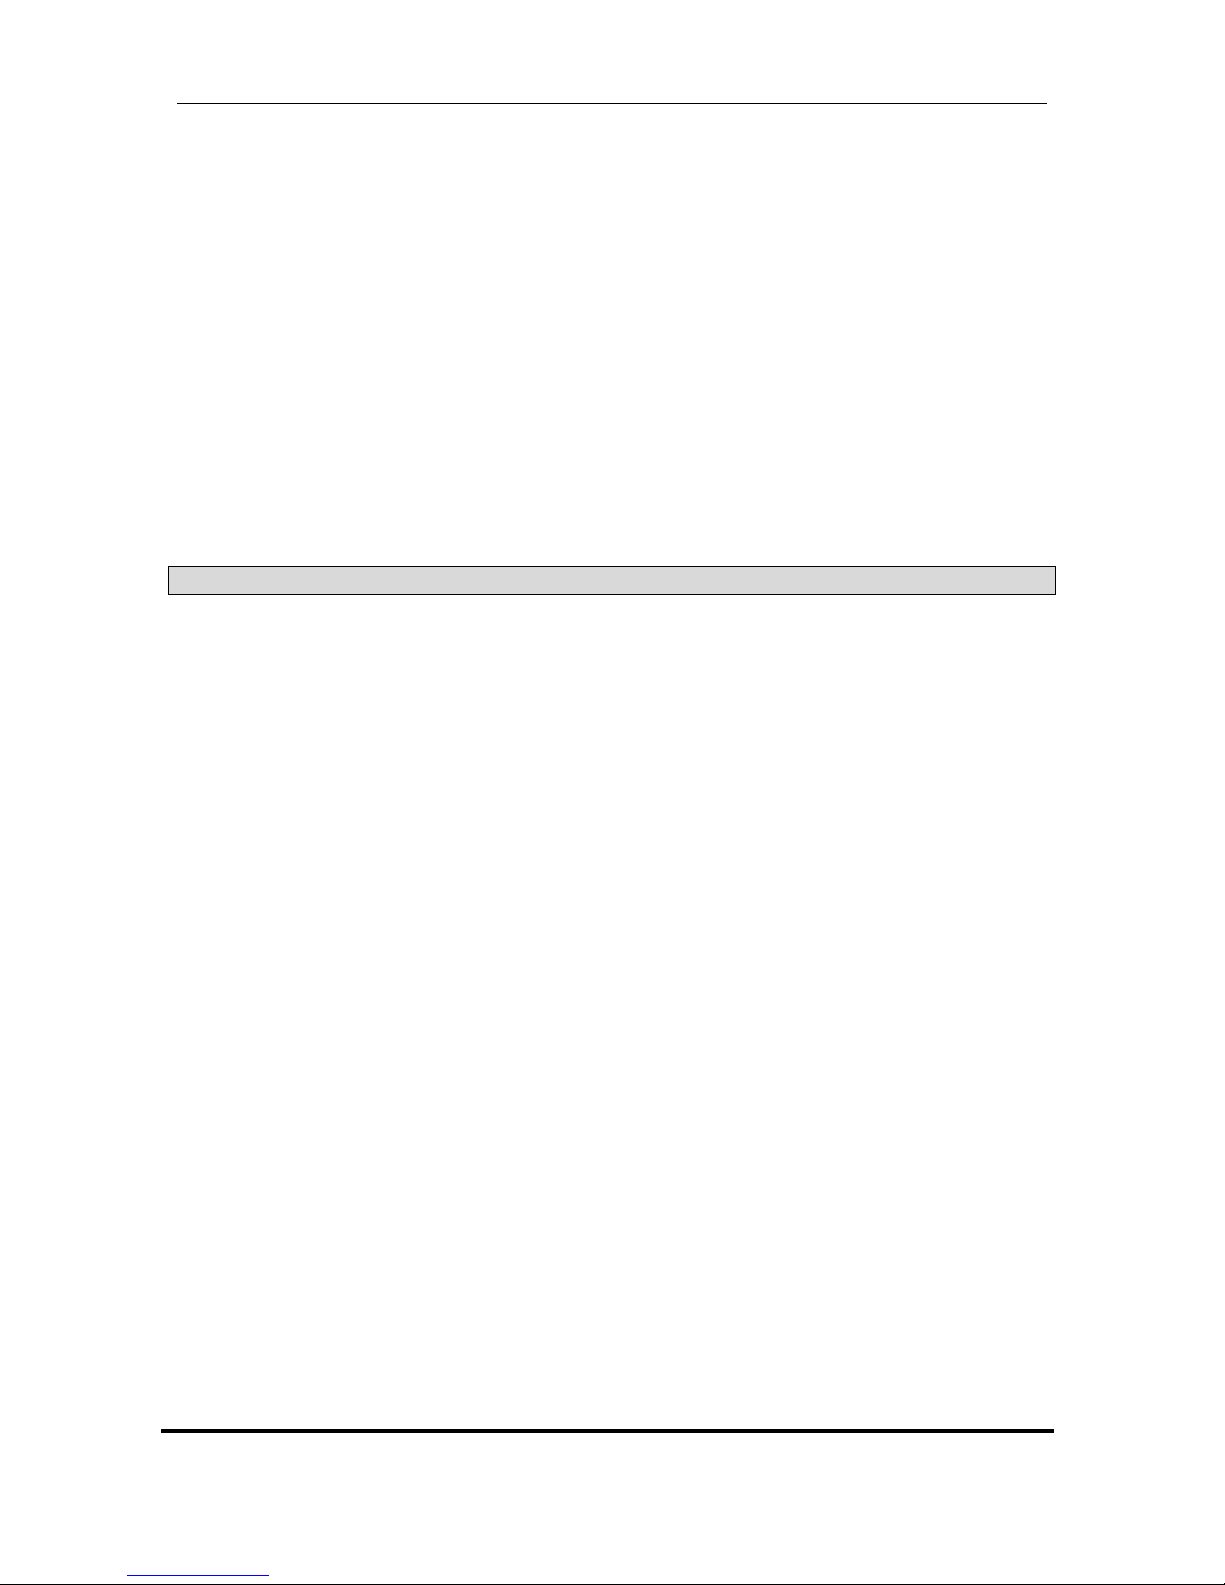
Open the Configuration folder and click the IP Address button. The web manager will display the Switch
IP Settings window below.
Figure 3-3. Switch IP Settings menu
NOTE: The Switch’s factory default IP address is 10.90.90.90 with a
subnet mask of 255.0.0.0 and a default gateway of 0.0.0.0.
36
Page 37
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
To manually assign the Switch’s IP address, subnet mask, and default gateway address:
1. Select Manual from the Get IP From drop-down menu.
2. Enter the appropriate IP address and subnet mask.
If you want to access the Switch from a different subnet from the one it is installed on, enter the IP address
of the gateway. If you will manage the Switch from the subnet on which it is installed, you can leave the
default address (0.0.0.0) in this field.
If no VLANs have been previously configured on the Switch, you can use the default VLAN ID (VID) 1.
The default VLAN contains all of the Switch ports as members. If VLANs have been previously configured
on the Switch, you will need to enter the VLAN ID of the VLAN that contains the port connected to the
management station that will access the Switch. The Switch will allow management access from stations
with the same VID listed here.
To use the BOOTP or DHCP protocols to assign the Switch an IP address, subnet mask, and default
gateway address:
Use the Get IP From pull-down menu to choose from BOOTP or DHCP. This selects how the Switch will
be assigned an IP address on the next reboot.
The Switch IP Settings options are:
Parameter Description
BOOTP
DHCP
Manual
Subnet Mask
The Switch will send out a BOOTP broadcast request when it is powered
up. The BOOTP protocol allows IP addresses, network masks, and
default gateways to be assigned by a central BOOTP server. If this option
is set, the Switch will first look for a BOOTP server to provide it with this
information before using the default or previously entered settings.
The Switch will send out a DHCP broadcast request when it is powered
up. The DHCP protocol allows IP addresses, network masks, and default
gateways to be assigned by a DHCP server. If this option is set, the
Switch will first look for a DHCP server to provide it with this information
before using the default or previously entered settings.
Allows the entry of an IP address, Subnet Mask, and a Default Gateway
for the Switch. These fields should be of the form xxx.xxx.xxx.xxx, where
each xxx is a number (represented in decimal form) between 0 and 255.
This address should be a unique address on the network assigned for use
by the network administrator. The fields which require entries under this
option are as follows:
A Bitmask that determines the extent of the subnet that the Switch is on.
Should be of the form xxx.xxx.xxx.xxx, where each xxx is a number
(represented in decimal) between 0 and 255. The value should be
255.0.0.0 for a Class A network, 255.255.0.0 for a Class B network, and
255.255.255.0 for a Class C network, but custom subnet masks are
allowed.
Default Gateway
IP address that determines where packets with a destination address
outside the current subnet should be sent. This is usually the address of a
router or a host acting as an IP gateway. If your network is not part of an
intranet, or you do not want the Switch to be accessible outside your local
network, you can leave this field unchanged.
VID
This allows the entry of a VLAN ID from which a management station will
be allowed to manage the Switch using TCP/IP (in-band via web manager
or Telnet). Management stations that are on VLANs other than the one
37
Page 38
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
entered in the VID field will not be able to manage the Switch in-band
unless their IP addresses are entered in the Security IP Management
menu. If VLANs have not yet been configured for the Switch, the default
VID (1) contains all of the Switch’s ports. There are no entries in the
Security IP Management table, by default − so any management station
that can connect to the Switch can access the Switch until either
Management Station IP Addresses (see page 38) are assigned or SNMP
settings are configured to control management.
Setting the Switch’s IP Address using the Console Interface
Each Switch must be assigned its own IP Address, which is used for communication with an SNMP
network manager or other TCP/IP application (for example BOOTP, TFTP). The Switch’s default IP
address is 10.90.90.90. You can change the default Switch IP address to meet the specification of your
networking address scheme.
The IP address for the Switch must be set before it can be managed with the Web-based manager. The
Switch IP address can be automatically set using BOOTP or DHCP protocols, in which case the actual
address assigned to the Switch must be known.
The IP address may be set using the Command Line Interface (CLI) over the console serial port as follows:
Starting at the command line prompt, enter the commands config ipif System ipaddress
xxx.xxx.xxx.xxx/yyy.yyy.yyy.yyy. Where the x’s represent the IP address to be assigned to the IP interface
named System and the y’s represent the corresponding subnet mask.
Alternatively, you can enter config ipif System ipaddress xxx.xxx.xxx.xxx/z. Where the x’s represent the
IP address to be assigned to the IP interface named System and the z represents the corresponding number
of subnets in CIDR notation.
The IP interface named System on the Switch can be assigned an IP address and subnet mask that can then
be used to connect a management station to the Switch’s Telnet or Web-based management agent.
The system message Success indicates that the command was executed successfully. The Switch can now
be configured and managed via Telnet and the CLI or via the Web-based management agent using the
above IP address to connect to the Switch.
Security IP Management Stations Configuration
Use the Security IP Management window to define up to four community strings. Community strings are
used to verify who can receive SNMP information from the Switch.
To access the Security IP Management window, click Trusted Host in the Security folder.
Figure 3-4. Security IP Management menu
Use the Management Station IP Settings to select up to three management stations used to manage the
Switch. If you choose to define one or more designated management stations, only the chosen stations, as
defined by IP address, will be allowed management privilege through the web manager or Telnet session.
38
Page 39
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
To define a management station IP setting, type in the IP address in the area provided and then click the
Apply button.
39
Page 40
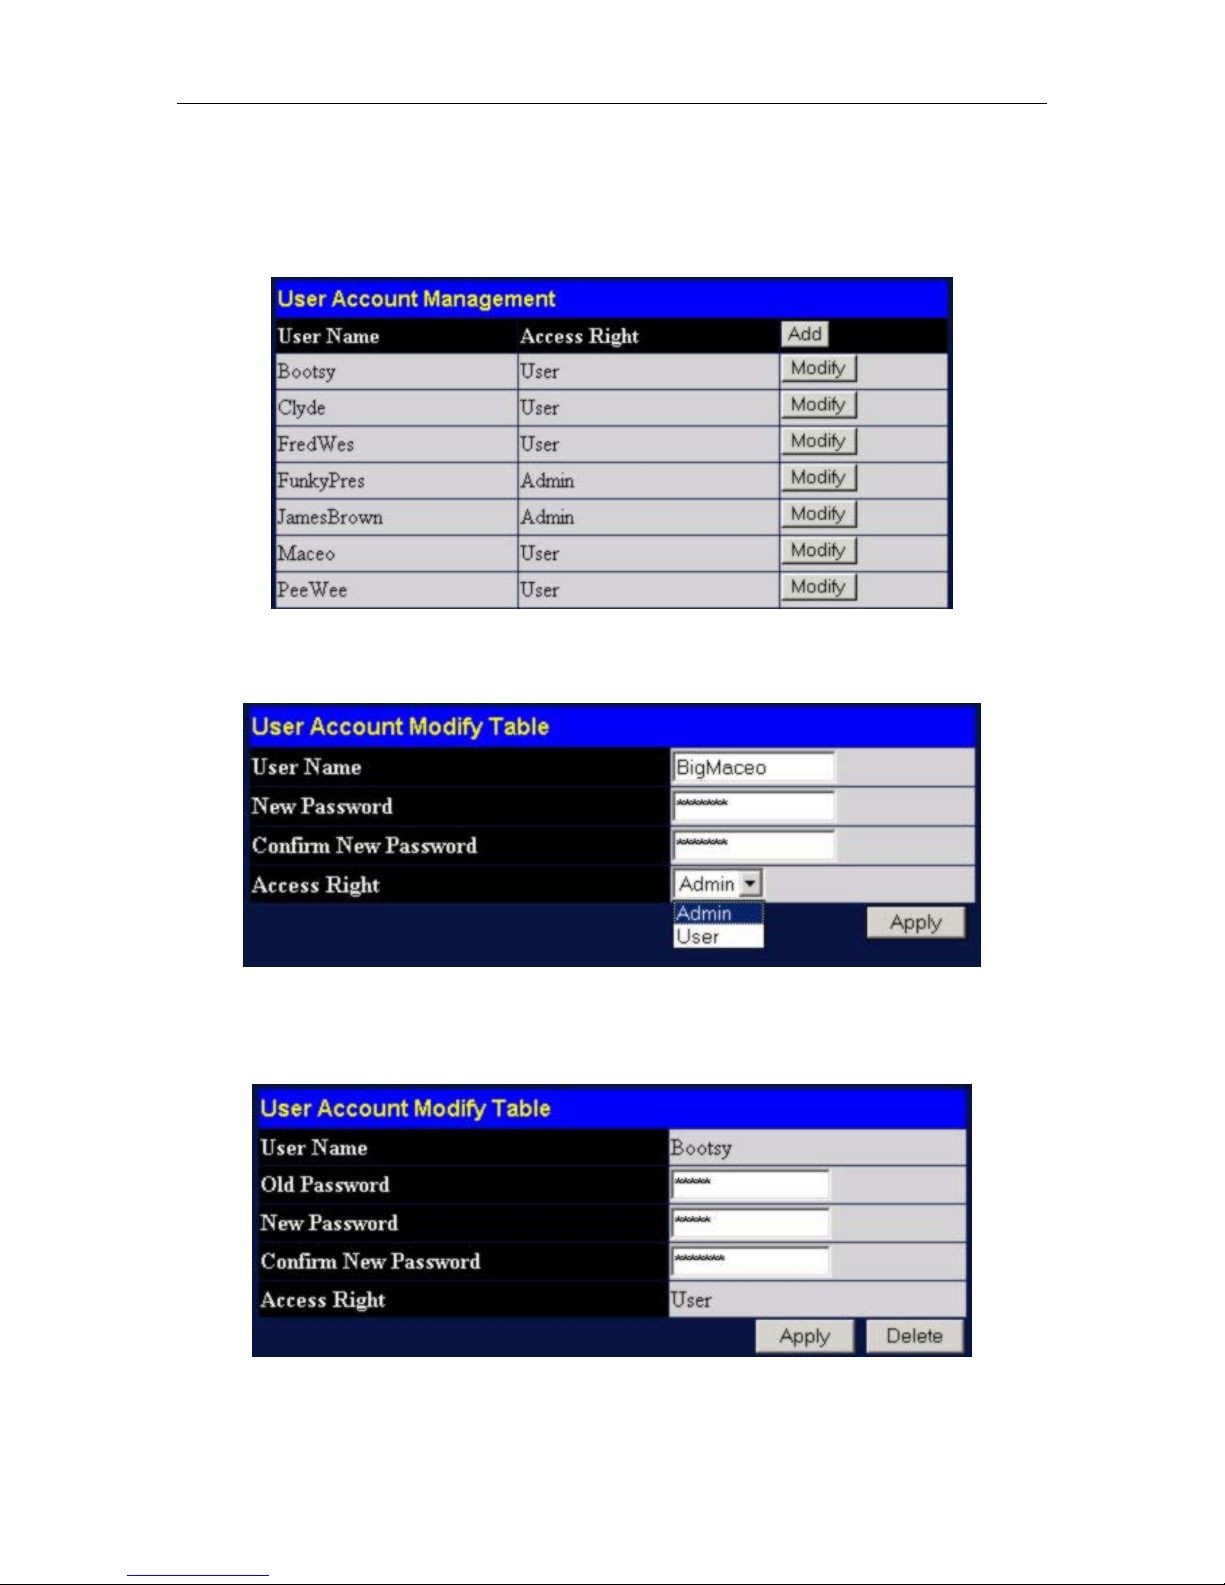
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
User Account Management
Use the User Account Management to control user privileges. To view existing User Accounts, open the
Management folder and click on the User Accounts link. This will open the User Account Management
window.
Figure 3-5. User Account Management table
To add a new user, click on the Add button in the User Account Management Table. To modify or delete
an existing user, click on the Modify button for that user.
Figure 3- 6. User Account Add menu
Add a new user by typing in a User Name, and New Password and retype the same password in the
Confirm New Password. Choose the level of privilege (Admin or User) from the Access Right drop-down
menu.
Figure 3- 7. User Account Modify menu
40
Page 41
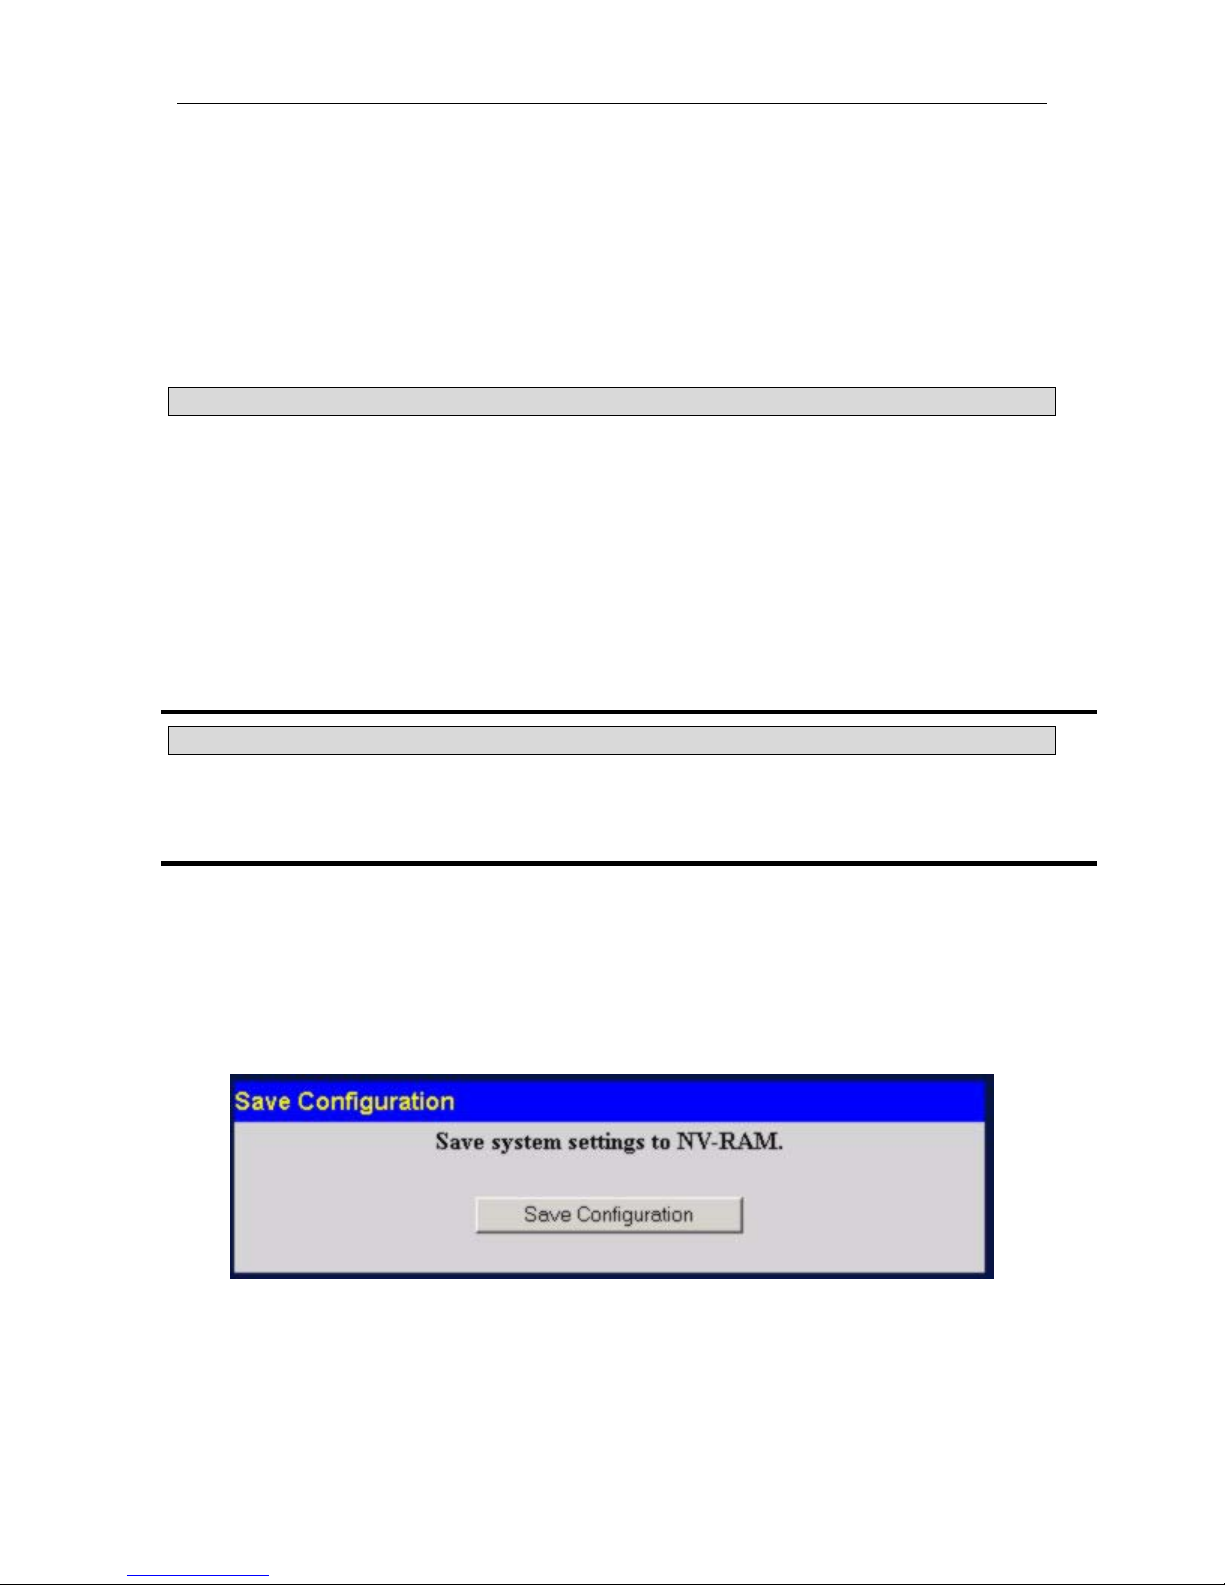
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Modify or delete an existing user account in the User Account Modify Table window. To delete the user
account, click on the Delete button. To change the password, type in the New Password and retype it in the
Confirm New Password entry field. Choose the level of privilege (Admin or User) from the Access Right
drop-down menu.
Admin and User Privileges
There are two levels of user privileges: Admin and User. Some menu selections available to users with
Admin privileges may not be available to those with User privileges.
The following table summarizes the Admin and User privileges:
Management Admin User
Configuration
Network Monitoring
Community Strings and Trap Stations
Update Firmware and Configuration Files
System Utilities
Factory Reset
User Account Management
Add/Update/Delete User Accounts
View User Accounts
Table 3- 1. Admin and User Privileges
After establishing a User Account with Admin-level privileges, be sure to save the changes (see below).
Yes Read Only
Yes Read Only
Yes Read Only
Yes No
Yes PING Only
Yes No
Yes No
Yes No
Save Changes
Changes made to the Switch’s configuration must be saved in order to retain them. Access the Save
Configuration window by clicking the Save Changes button located in the Maintenance folder.
The Switch has two levels of memory, normal RAM and non-volatile or NV-RAM. To save all the changes
made in the current session to the Switch’s flash memory, click the Save Configuration button. Click the
OK button in the new dialog box that appears to continue. When this is done, the settings will be
immediately applied to the Switching software in RAM, and will immediately take effect. Once the Switch
Figure 3- 8. Save Configuration menu
41
Page 42
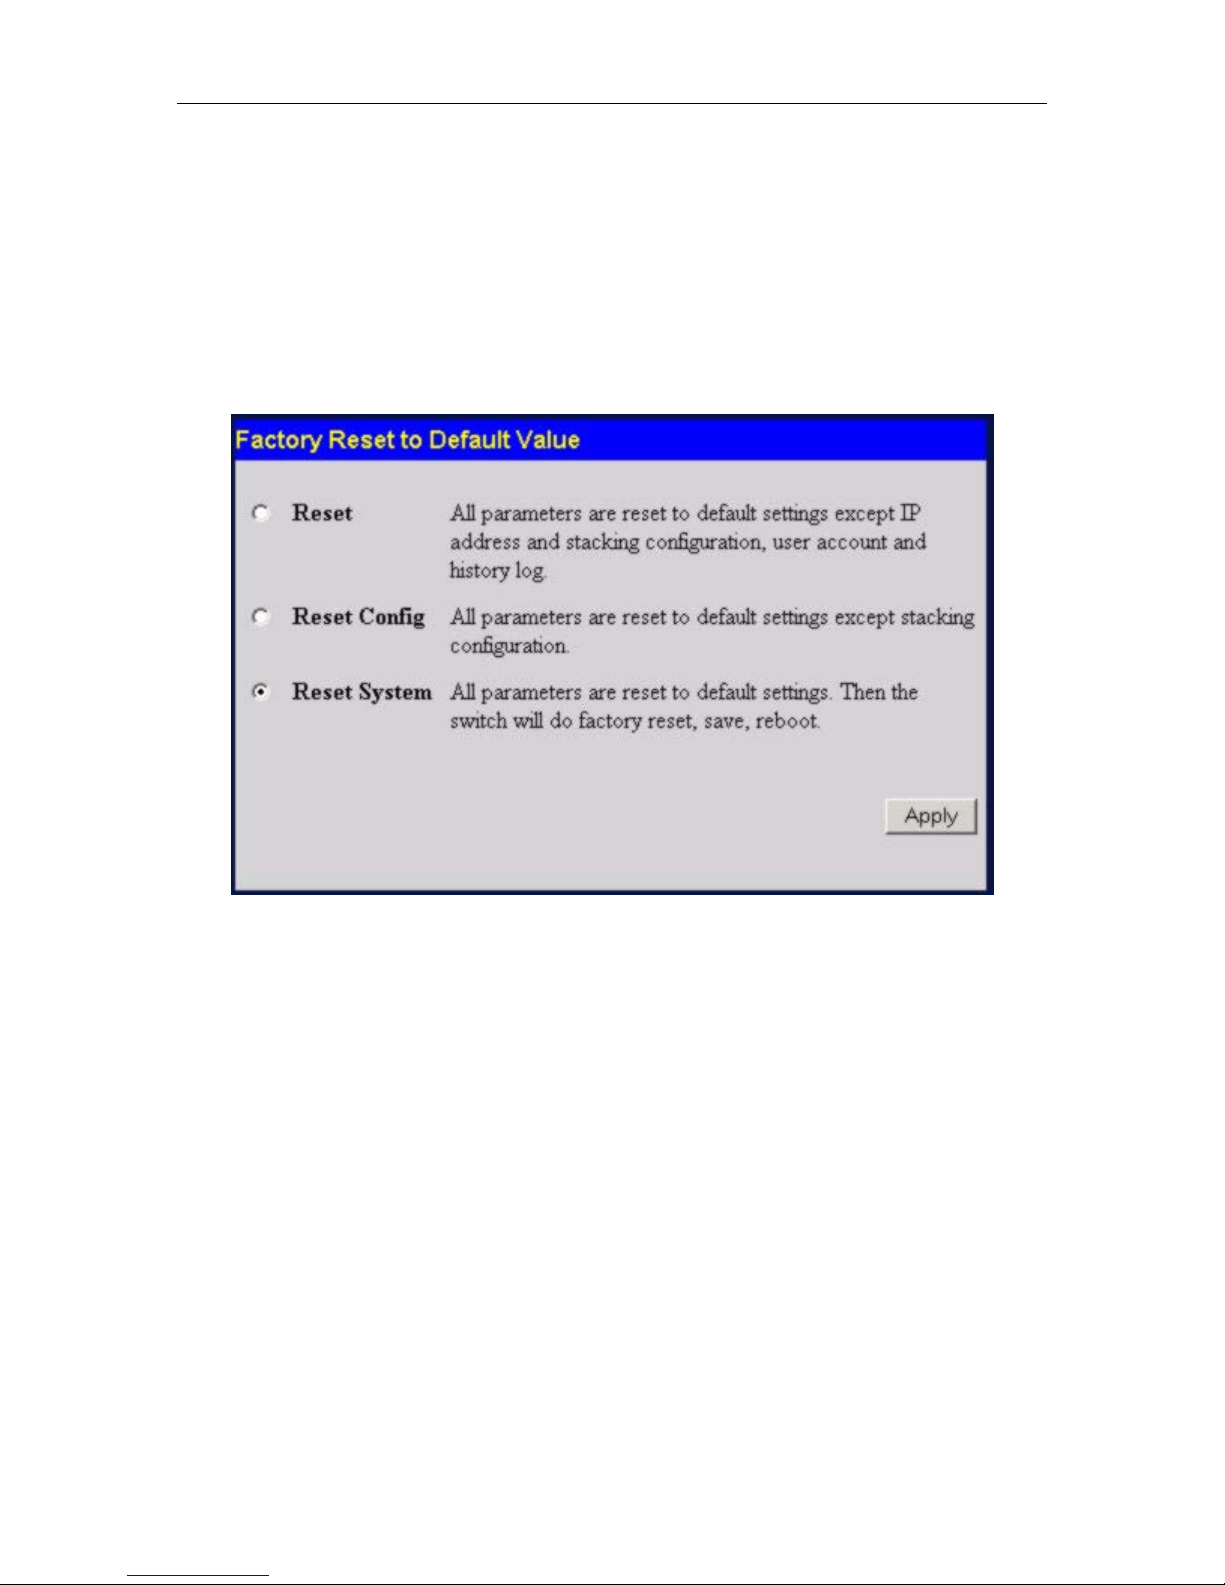
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
configuration settings have been saved to NV-RAM, they become the default settings for the Switch. These
settings will be used every time the Switch is rebooted.
Some settings, though, require you to restart the Switch before they will take effect. Restarting the Switch
erases all settings in RAM and reloads the stored settings from the NV-RAM. Thus, it is necessary to save
all setting changes to NV-RAM before rebooting the Switch.
Factory Reset
Click the Factory Reset link in the Maintenance folder to bring up the following window.
Figure 3- 9. Factory Reset to Default Value menu
The following options are available to perform a factory reset:
Reset − Returns all configuration settings to the factory default settings except the Switch’s stacking mode,
IP address, subnet mask, and default gateway settings.
Reset Config − Returns all configuration settings to the factory default settings except the stacking mode
configuration, but does not save the settings or reboot the Switch. If you select this option the Switch
configuration will be returned to the factory default settings for the current session only. When the Switch
is rebooted, it will return to the last configuration saved to the Switch’s NV-RAM using the Save Changes
option.
• Reset System − Returns all configuration settings to the factory default settings, but does not save the
settings or reboot the Switch. If you select this option the Switch configuration will be returned to the
factory default settings and then saves the factory default configuration to the Switch’s NV-RAM. The
Switch will then reboot. When the Switch has rebooted, it will have the same configuration as when it
was delivered from the factory.
Select the reset option you want to perform and click on the Apply button.
42
Page 43

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Restart System
The following window is used to restart the Switch. Access this window by clicking on the Restart System
link in the Maintenance folder.
Click the Yes after “Do you want to save the settings?” to instruct the Switch to save the current
configuration to non-volatile RAM before restarting the Switch.
Clicking the No option instructs the Switch not to save the current configuration before restarting the
Switch. All of the configuration information entered from the last time Save Changes was executed will
be lost.
Click the Restart button to restart the Switch.
NOTE: Clicking Yes is
equivalent to executing
Save Changes and then
restarting the Switch.
Figure 3- 10. Restart System menu
43
Page 44
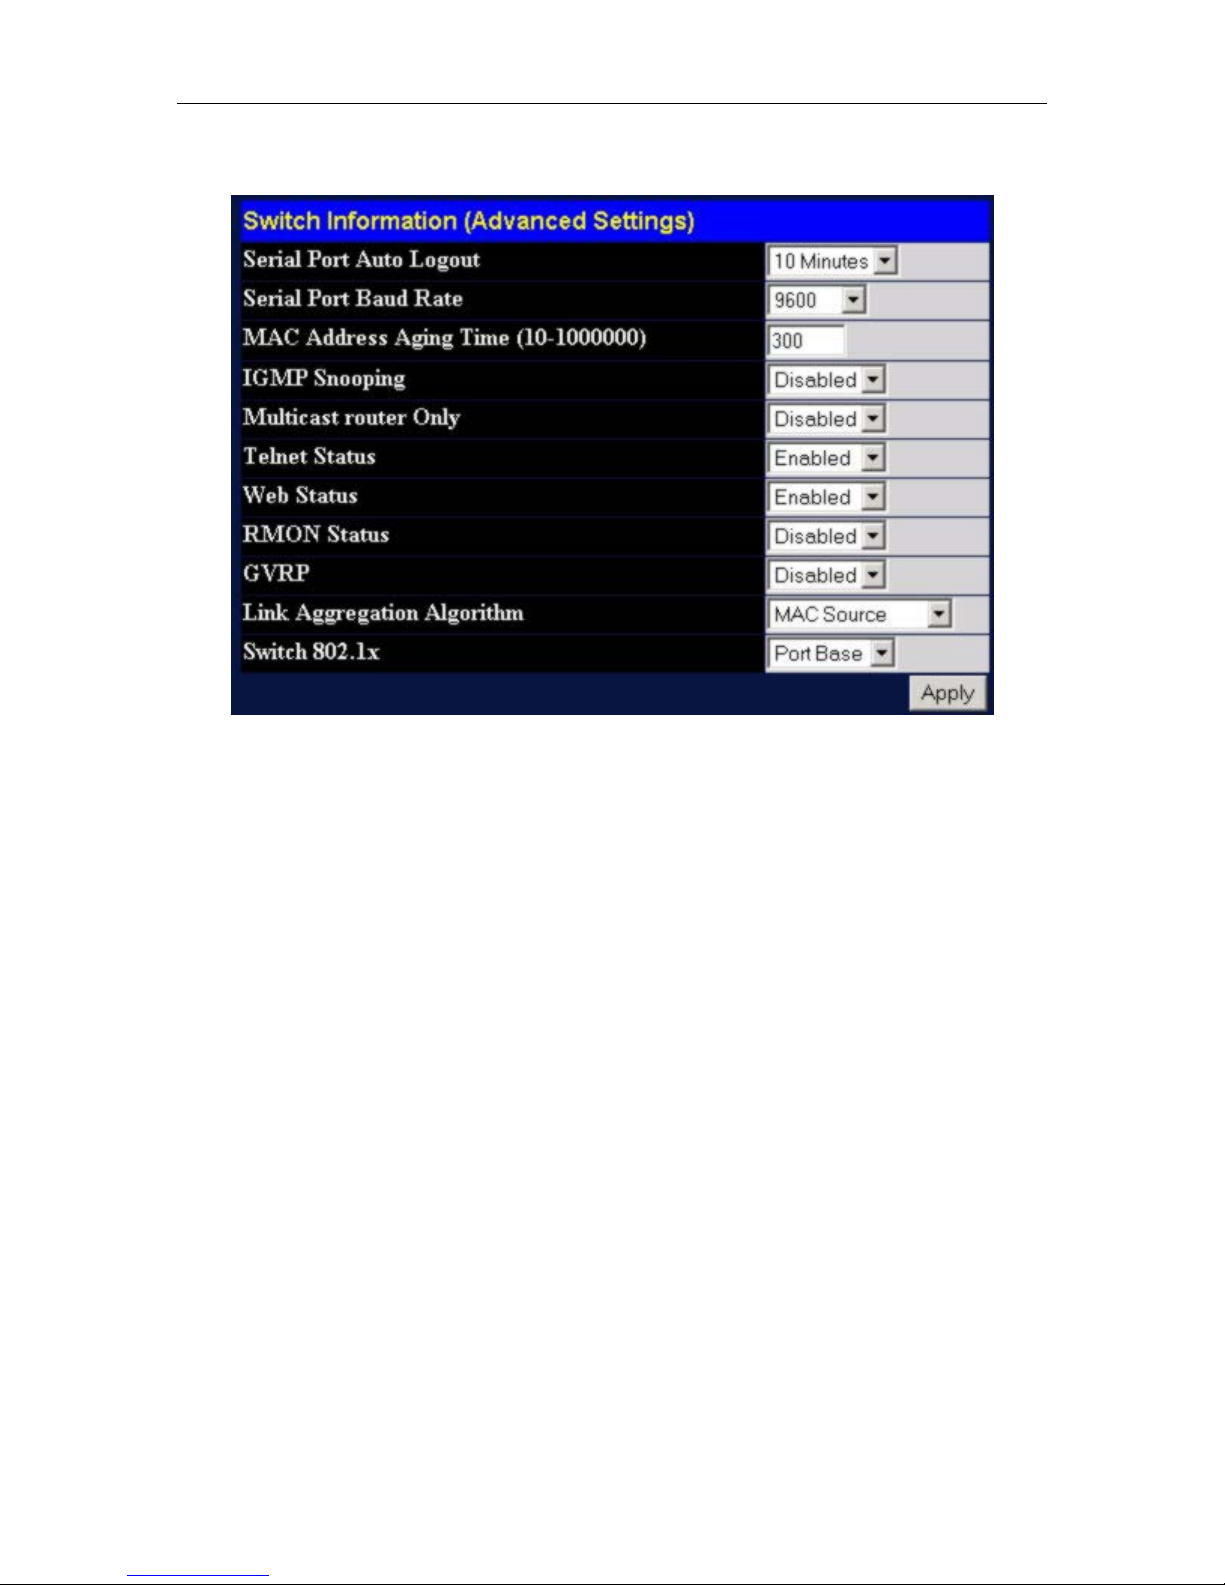
Advanced Settings
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 3- 11. Switch Information (Advanced Settings) menu
44
Page 45

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The Advanced Settings options are summarized in the table below:
Parameter Description
Serial Port Auto
Logout
Serial Port Baud
Rate
MAC Address
Aging Time (10-
1000000)
IGMP Snooping
Multicast router
Only
Telnet Status
Select the logout time used for the console interface. This automatically
logs the user out after an idle period of time as defined. Choose from the
following options: 2 Minutes, 5 Minutes, 10 Minutes, 15 Minutes or Never.
Select the baud rate used for the console interface. This automatically
logs the user out after an idle period of time as defined. Choose from the
following options: 9600, 19200, 38400 or 115200.
This field specifies the length of time a learned MAC Address will remain
in the forwarding table without being accessed (that is, how long a learned
MAC Address is allowed to remain idle). The default age-out time for the
Switch is 300 seconds. To change this, type in a different value
representing the MAC address age-out time in seconds. The Aging Time
can be set to any value between 10 and 1,000,000 seconds.
To enable system-wide IGMP Snooping capability select Enabled. IGMP
snooping is Disabled by default. Enabling IGMP snooping allows you to
specify use of a multicast router only (see below). To configure IGMP
Snooping for individual VLANs, use the IGMP Snooping window in the
IGMP folder.
If this option is enabled and IGMP Snooping is also enabled, the Switch
forwards all multicast traffic to a multicast-enabled router only. Otherwise,
the Switch will forward all multicast traffic to any IP router.
Telnet configuration is Enabled by default. If you do not want to allow
configuration of the system through Telnet choose Disabled.
Telnet TCP Port
Number(1-65535)
Web Status
Web TCP Port
Number(1-65535)
RMON Status
GVRP
Link Aggregation
Algorithm
Switch 802.1x
Syslog state
The Telnet TCP port number. TCP ports are numbered between 1 and
65535. The "well-known" TCP port for the Telnet protocol is 23.
Web-based management is Enabled by default. If you choose to disable
this by selecting Disabled, you will lose the ability to configure the system
through the web interface as soon as these settings are applied.
The TCP port number currently being utilized by the Switch to connect to
the web interface. The "well-known" TCP port for the Web interface is 80.
Remote monitoring (RMON) of the Switch is Enabled or Disabled here.
Use this pull-down menu to enable or disable GVRP on the Switch.
The algorithm that the Switch uses to balance the load across the ports
that make up the port trunk group is defined by this definition. Choose
MAC Source, MAC Destination, MAC Src & Dest, IP Source, IP
Destination, and IP Src & Dest. (See Link Aggregation)
Use this pull-down menu to enable or disable 802.1x functions on the
Switch.
Use this pull-down menu to enable or disable Syslog.
45
Page 46

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Stack Information
The GSW-1290 Switch can be used as a standalone high-capacity Switch or be used in a stacked
arrangement. There are two hardware requirements to use the Switch in a stacked group:
1. The proper module(s) must be installed. One or two MDU-1290S Stacking modules must be installed in
order to use the GSW-1290 Switch in a stacked configuration.
2. The Slave Switch units must be the GSW-2492 equipped with a Stacking module.
3. Two MDU-1290S Stacking modules can be installed on the GSW-1290 to allow up to eight
2492 Switches to be stacked. The four built-in combination ports may also be used as stacking ports.
Therefore it is possible to stack twelve GSW-2492 Switches with a GSW-1290.
GSW-
The web manager can be used to enable or disable the stacking mode and to enable stacking for any of the
built-in combination ports.
The Switch stack displayed in the upper right-hand corner of your web-browser is a virtual representation
of the actual stack (see example below). The icons appear in the same order as their respective Switches.
When the Switches are properly interconnected, information about the resulting Switch stack is displayed
in the Stack Mode Setup window. To view stacking information or to enable/disable the stacking mode,
click the Stack Information link in the Configuration folder.
Figure 3- 12. Stack Mode Setup (stacking disabled) window
To enable the stacking mode, follow the steps listed below.
1. Select Enabled from the Stack Mode State drop-down menu.
2. Click on the Apply button.
To enable stacking for one or more built-in combination ports, do the following:
1. Select Enabled from the Stack Mode State drop-down menu.
2. Select the Stack Port by clicking to check a corresponding selection box.
46
Page 47
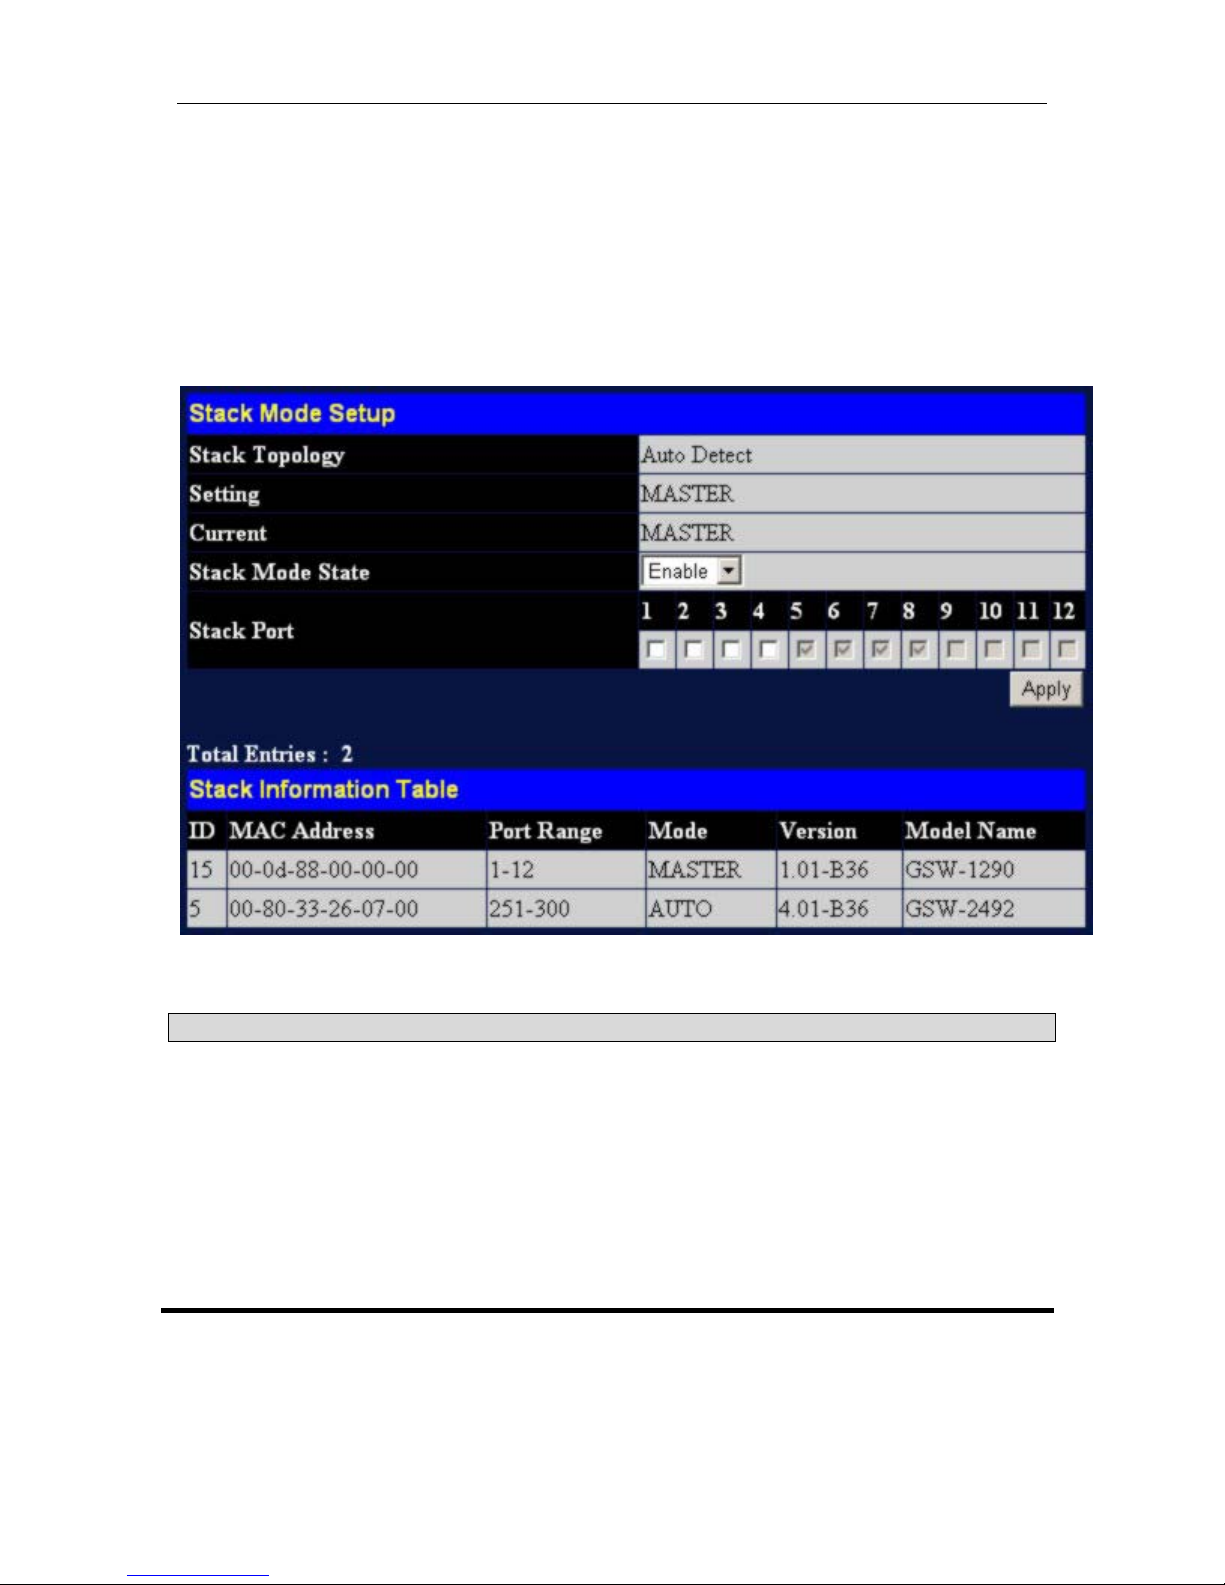
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The Stack Information Table displays the read-only information listed in the table on the next page.
The current order in the Switch stack is also displayed on the front panel of each slave Switch, under the
STACK NO. heading. The Stack ID LED display on the front panel of the GSW-1290 will always display
an F (15 in hex), regardless of whether the GSW-1290 is the master Switch in a Switch stack or in
standalone mode.
Below is an example of the Stack Mode Setup window with stacking mode enabled on Ports 5-8.
Figure 3- 13. Stack Mode Setup menu and Information table (stacking enabled)
Variables in this window are described below:
Parameter Description
ID
MAC Address
Port Range
Mode
Version
Model Name
Displays the Switch’s order in the stack. The Switch with a unit id of 1 is
the master Switch.
Displays the unique address of the Switch assigned by the factory.
Displays the total number of ports on the Switch. Note that the stacking
port is included in the total count.
Displays the method used to determine the stacking order of the Switches
in the Switch stack.
Displays the version number of the stacking firmware.
Displays the model name of the corresponding Switch in a stack.
47
Page 48
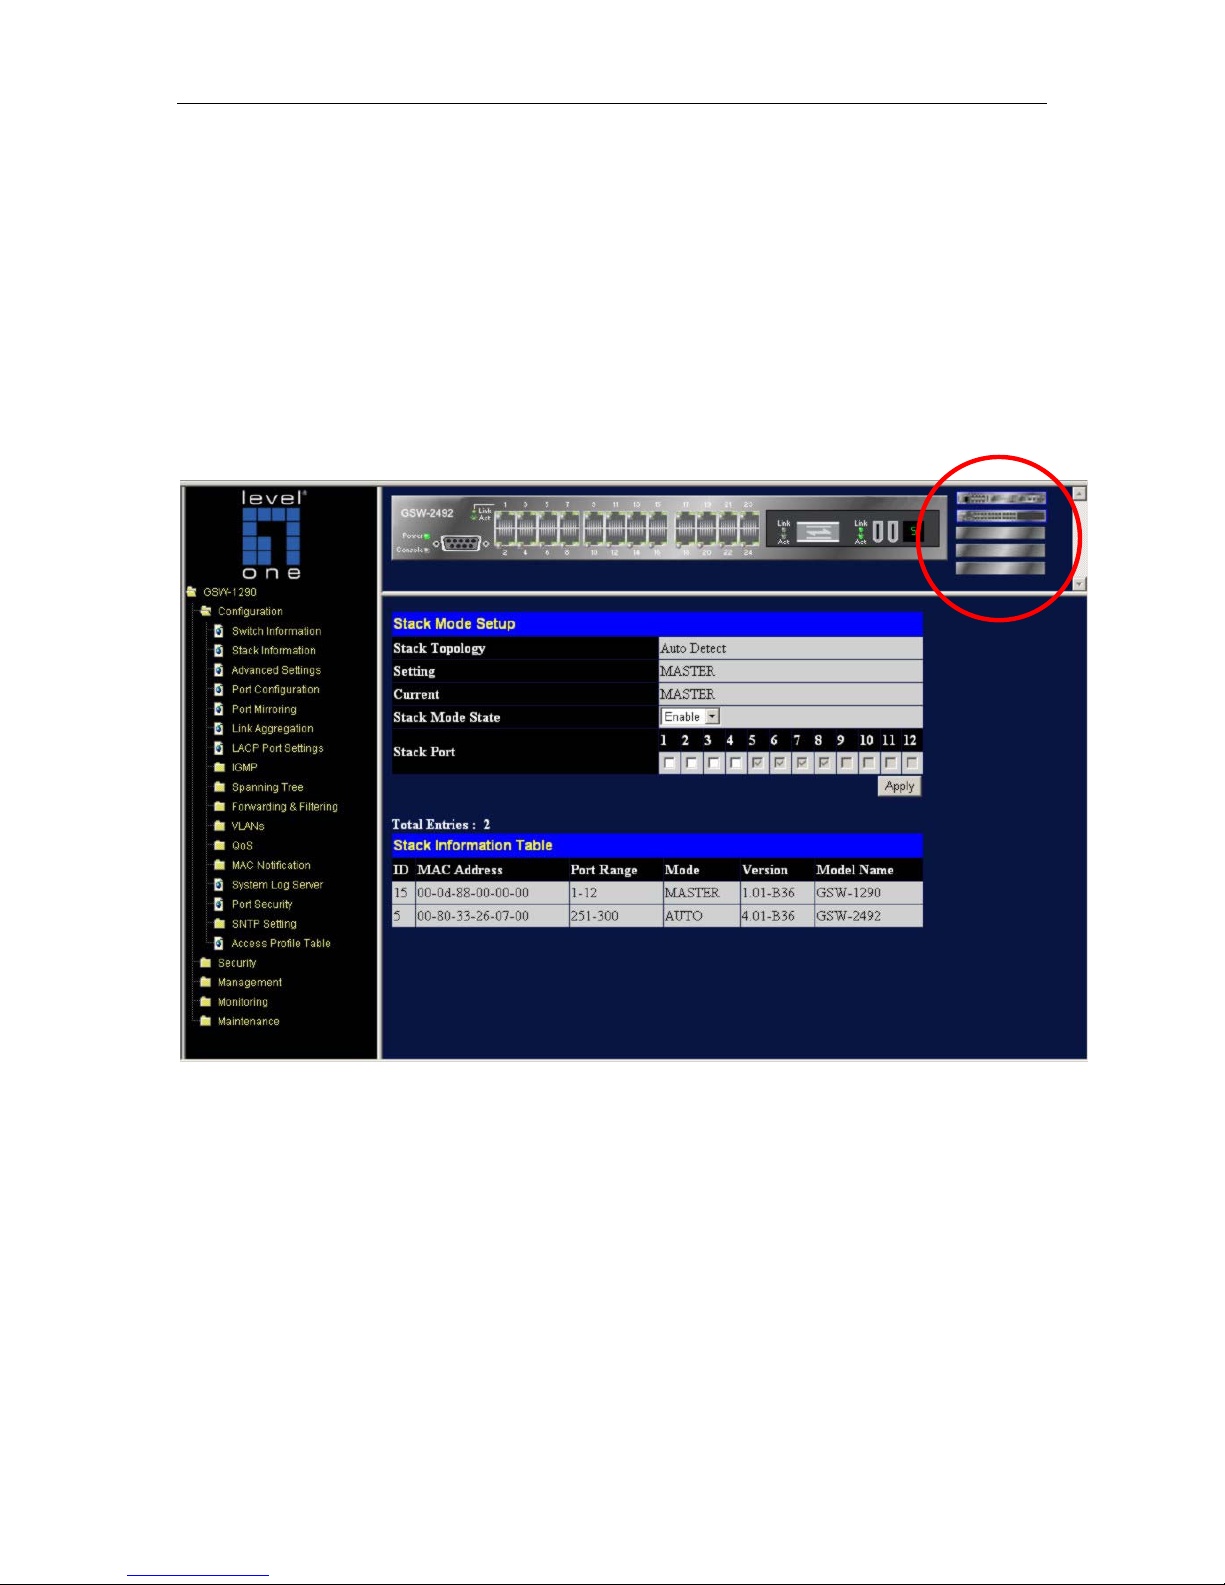
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
When the stacked group is connected and properly configured, the virtual stack appears in the upper righthand corner of the web page. Click on any unit in the virtual stack to see the real time display of the front
panel of that unit.
Figure 3- 14. Stack Information web page
48
Page 49
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Chapter 4
System Configuration
Port Configuration
Port Mirroring
Link Aggregation
LACP Port Settings
IGMP
IGMP Snooping
Static Router Ports Entry
Spanning Tree
STP Switch Settings
STP Port Settings
Forwarding & Filtering
Unicast Forwarding
Multicast Forwarding
Multicast Port Filtering Mode
VLANs
Static VLAN Entry
GVRP Setting
QoS
802.1p Default Priority
802,1p User Priority
QoS Output Scheduling
Traffic Segmentation
Bandwidth Control
MAC Notification
Global Settings
Port Settings
System Log Server
Port Security
SNTP Setting
Time Setting
Time Zone and DST
Access Profile Table
The GSW-1290’s Web interface is divided into six main folders: Configuration, Security, Management,
Monitoring, Maintenance, and Single IP Management. This chapter describes all of the Configuration
sub-folders and windows.
49
Page 50
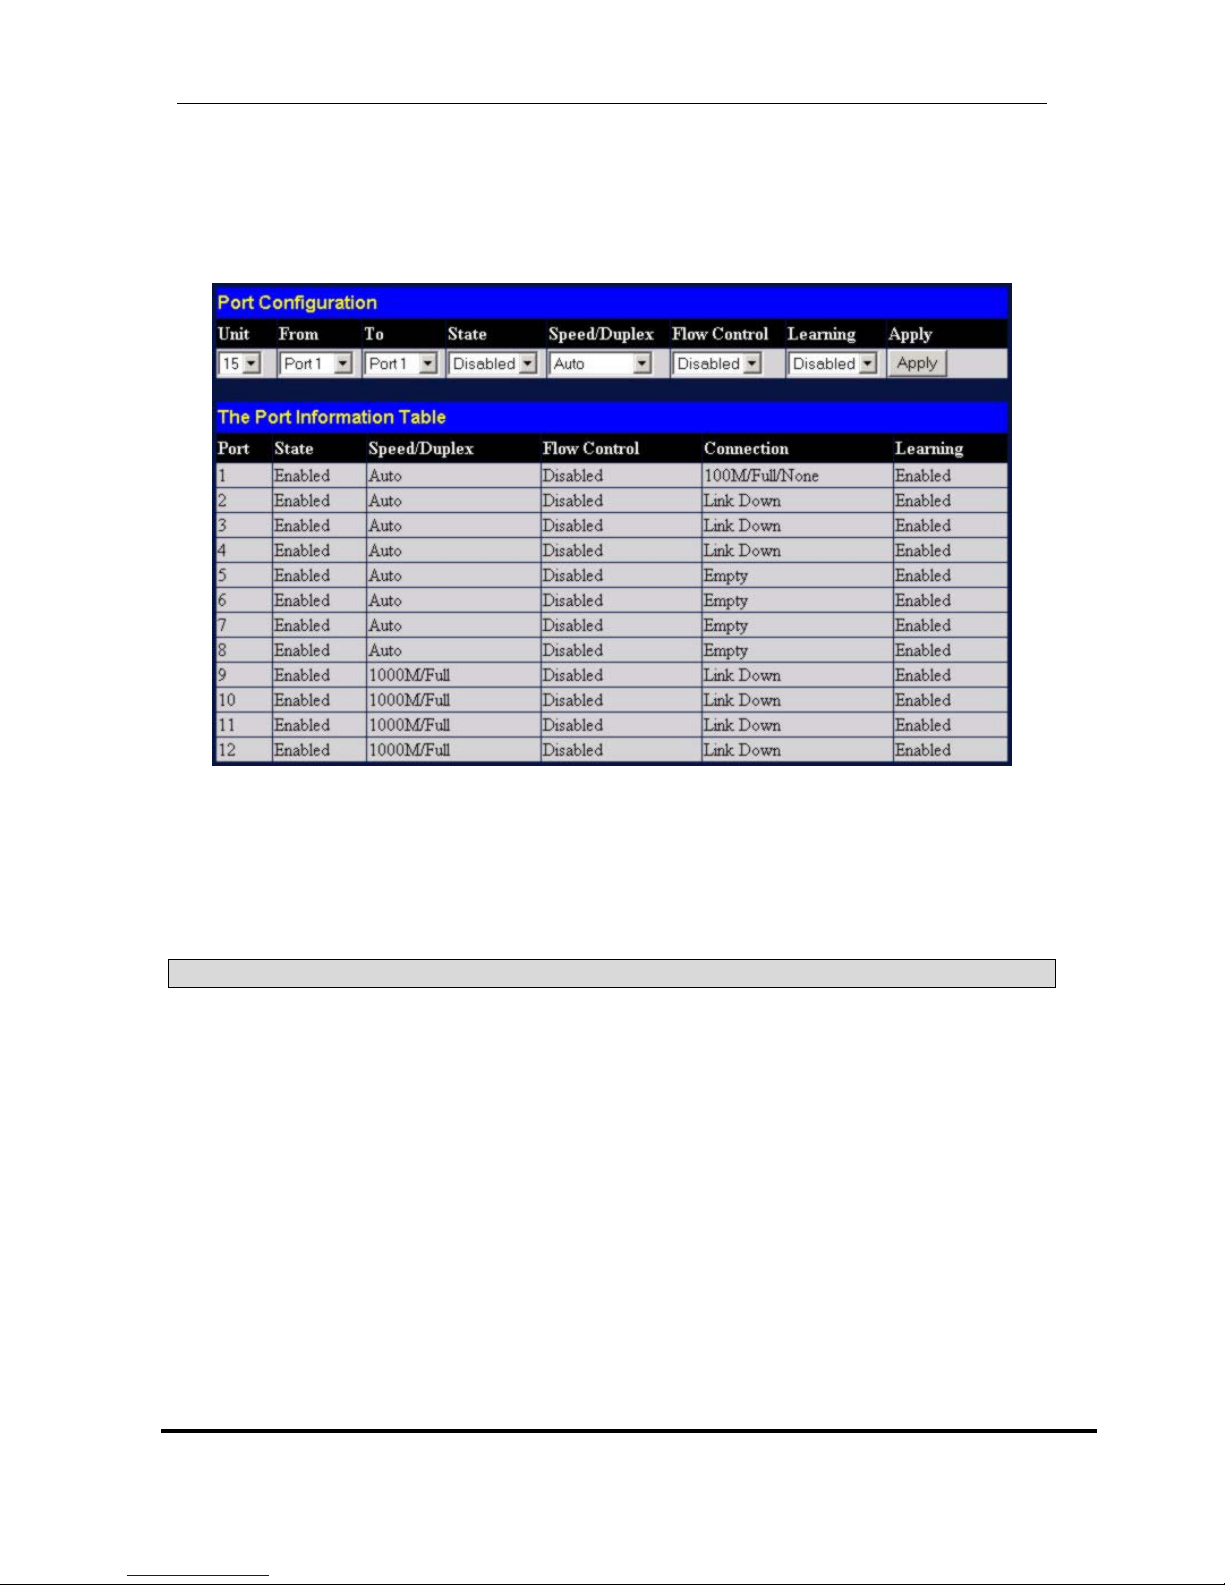
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Port Configuration
To configure basic port settings such as port speed, duplex, and learning state, use the Port Configuration
window.
Click the Port Configuration link in the Configuration folder:
Figure 4- 1. Port Configuration and Information table
To configure Switch ports:
1. Choose the Unit from the pull-down menu.
2. Choose the port or sequential range of ports using the From…To… port pull-down menus.
3. Use the remaining pull-down menus to configure the parameters described in the table below.
The configurable parameters for ports include the following:
Parameter Description
State <Enabled> Toggle the State field to either enable or disable a given port.
Speed/Duplex <Auto> Toggle the Speed/Duplex field to either select the speed and
duplex/half-duplex state of the port. Auto – auto-negotiation between
10 and 100 Mbps devices, full- or half-duplex. The Auto setting
allows the port to automatically determine the fastest settings the
device the port is connected to can handle, and then to use those
settings. The other options are 1000M/Full, 1000M/Half, 100M/Full,
100M/Half, 10M/Full, and 10M/Half. There is no automatic
adjustment of port settings with any option other than Auto.
Flow Control
Displays the flow control scheme used for the various port
configurations. Ports configured for full-duplex use 802.3x flow
control, half-duplex ports use backpressure flow control, and Auto
ports use an automatic selection of the two. The default is Disabled.
Learning
Enable or disable MAC address learning for the selected ports. When
Enabled, destination and source MAC addresses are automatically
50
Page 51
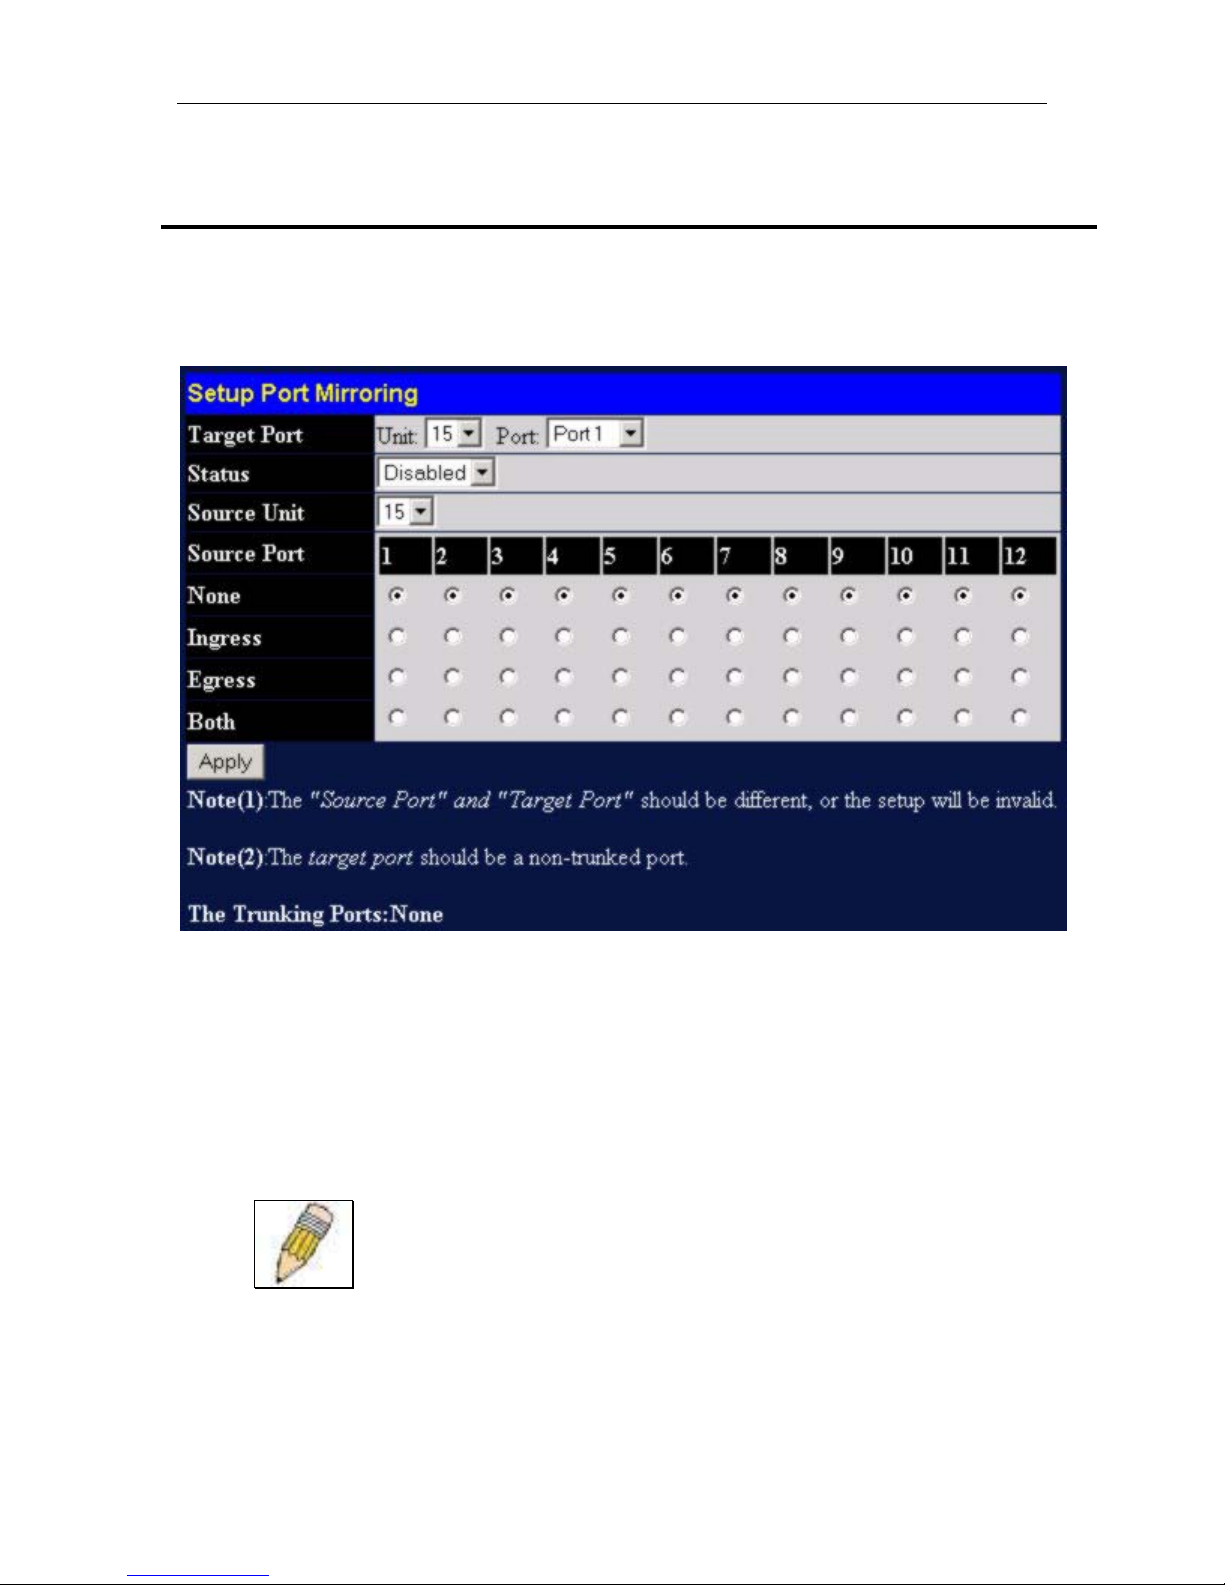
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
listed in the forwarding table. When learning is Disabled, MAC
addresses must be manually entered into the forwarding table. This
is sometimes done for reasons of security or efficiency.
Port Mirroring
The Switch allows you to copy frames transmitted and received on a port and redirect the copies to another
port. You can attach a monitoring device to the mirrored port, such as a sniffer or an RMON probe, to view
details about the packets passing through the first port. Follow the steps below to set up port mirroring.
Figure 4- 2. Setup Port Mirroring menu
To configure a mirror port:
Select the Source Unit containing the port that is being mirrored.
Configure how the port is to be mirrored by selecting the direction that will be mirrored. Choose Ingress,
Egress, or Both for the mirrored port by clicking the appropriate radio button for the port.
Select the Target Port using the Unit and Port drop-down menus.
Change the Status drop-down menu to Enabled.
Click Apply to let the changes take effect.
NOTE: You cannot mirror a fast port onto a slower port. For example, if you try
to mirror the traffic from a 100 Mbps port onto a 10 Mbps port, this can cause
throughput problems. The port you are copying frames from should always
support an equal or lower speed than the port to which you are sending the copies.
Also, the target port for the mirroring cannot be a member of a trunk group.
Please note a target port and a source port cannot be the same port.
51
Page 52
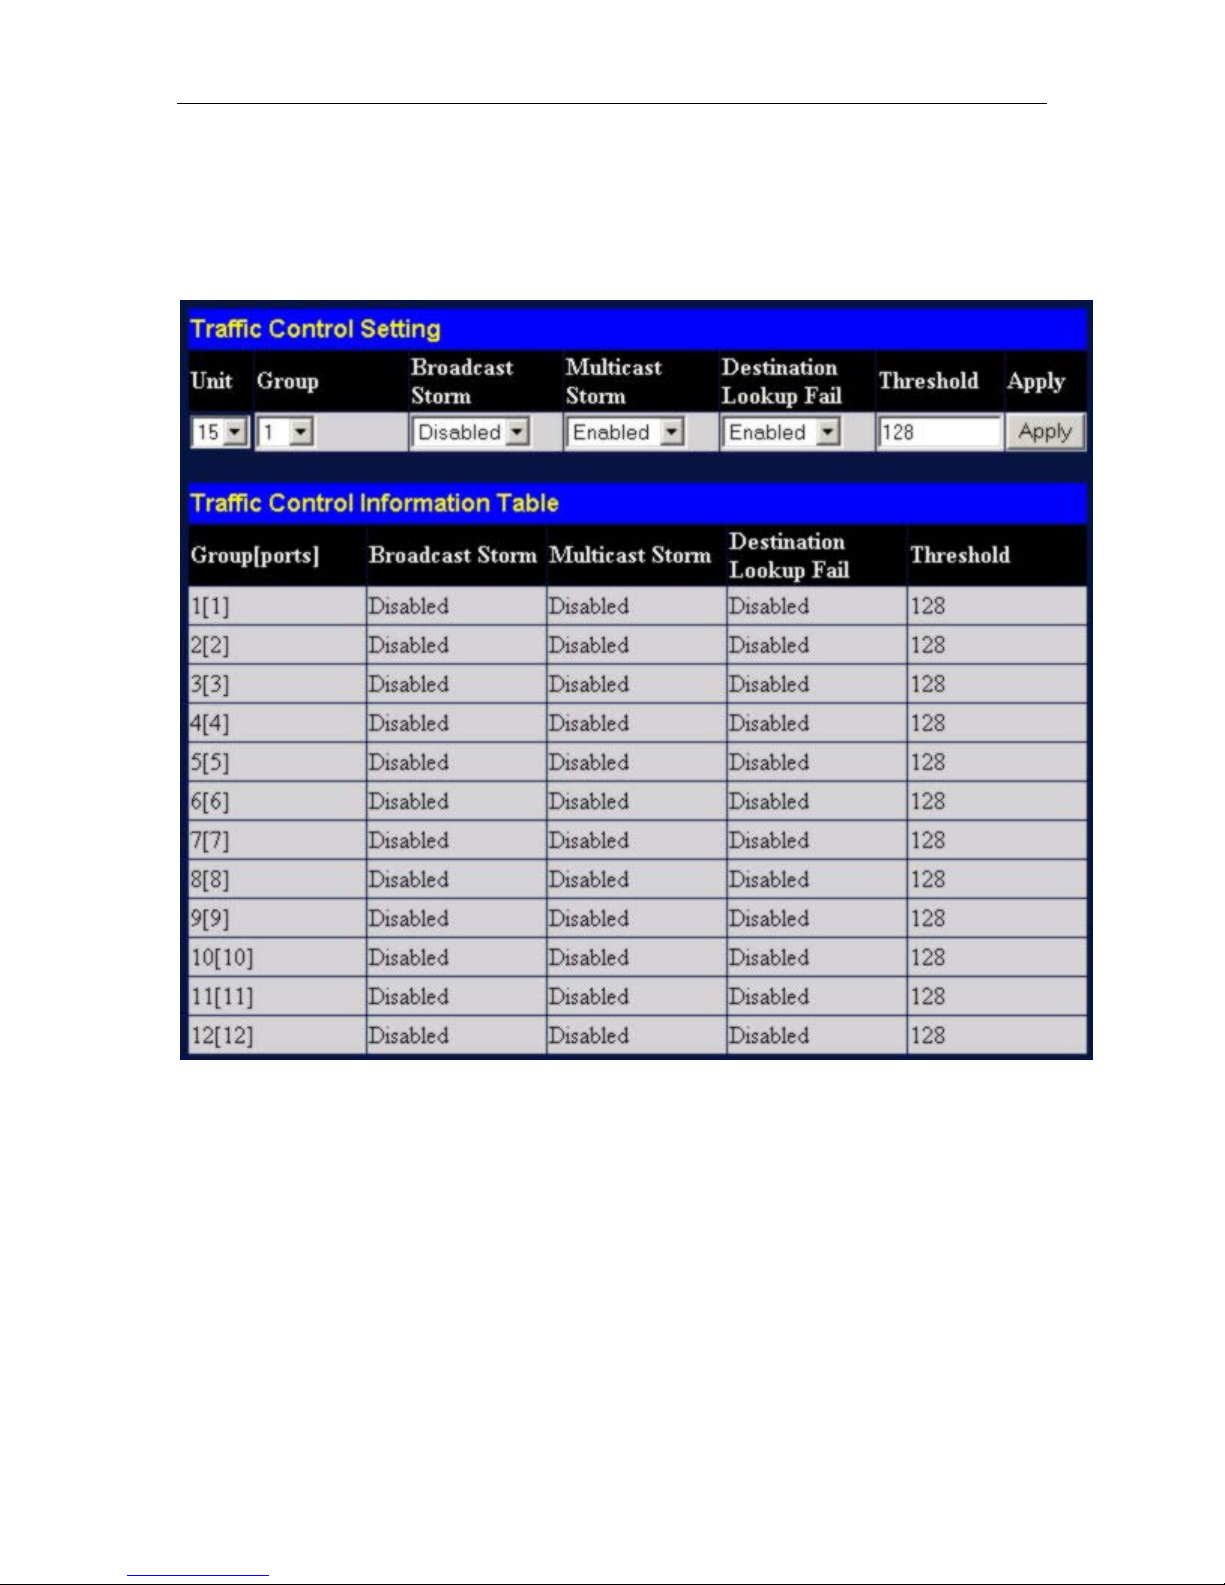
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Traffic Control
Use the Traffic Control Setting window to enable or disable storm control and adjust the threshold for
multicast and broadcast storms, as well as DLF (Destination Look Up Failure). Traffic control settings are
applied to individual Switch modules. The Traffic Control Setting menu is located in the QoS directory.
Open the QoS folder in the Configuration folder and click the Traffic Control link.
Figure 4- 3. Traffic Control Setting menu and Information table
Traffic or storm control is used to stop broadcast, multicast or ARP request storms that may result when a
loop is created. The Destination Look Up Failure control is a method of shutting down a loop when a storm
is formed because a MAC address cannot be located in the Switch’s forwarding database and it must send a
packet to all ports or all ports on a VLAN.
To configure Traffic Control, select the Unit (Unit ID of a Switch in a Switch stack − 15 for a Switch in
standalone mode) you want to configure. Broadcast Storm, Multicast Storm and Destination Look Up
Failure may be Enabled or Disabled. The Threshold value is the upper threshold at which the specified
traffic control is switched on. This is the number of Broadcast, Multicast or DLF packets, in Kbps, received
by the Switch that will trigger the storm traffic control measures. The Threshold value can be set from 0 to
255 packets. The Default setting is 128.
52
Page 53
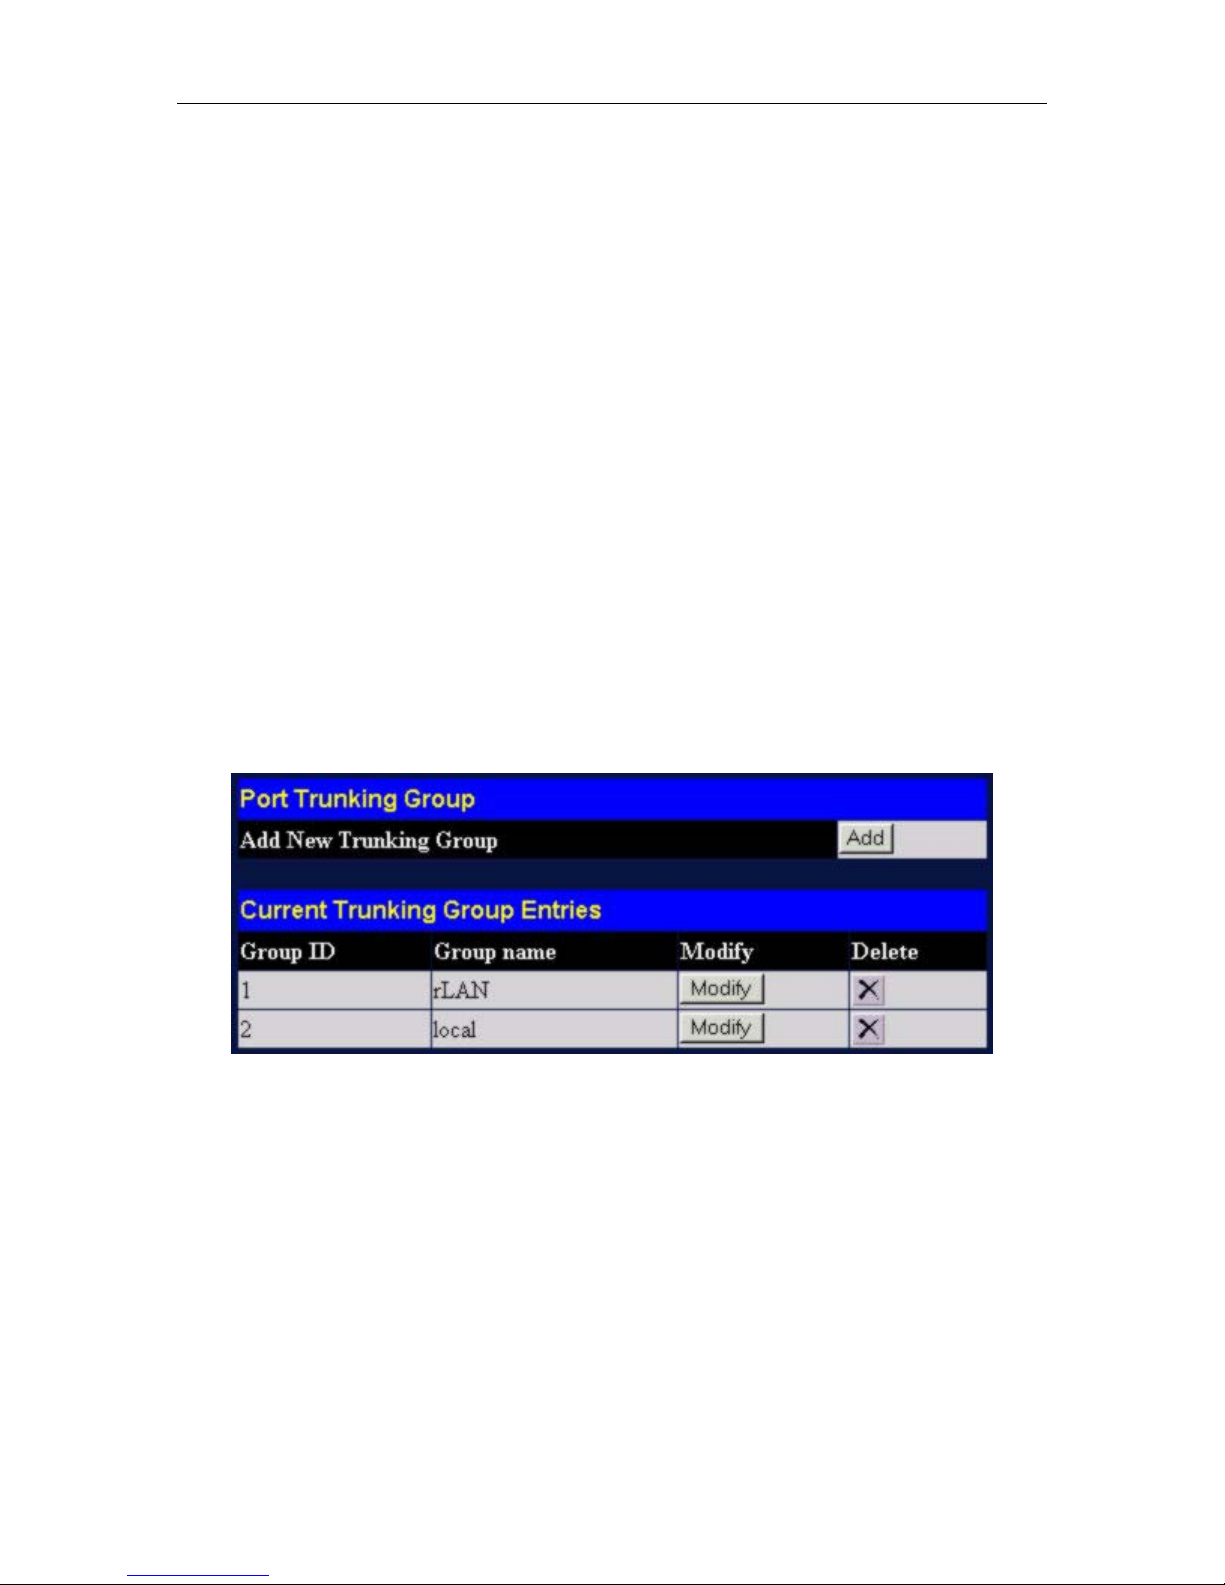
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Link Aggregation
Link aggregation allows several ports to be grouped together and to act as a single link. This gives a
bandwidth that is a multiple of a single link’s bandwidth.
Link aggregation is most commonly used to link a bandwidth intensive network device or devices – such as
a server – to the backbone of a network.
The Switch allows the creation of up to six link aggregation groups, each group consisting of up of up to
eight links (ports). The aggregated links must be contiguous (they must have sequential port numbers)
except the two (optional) Gigabit ports – which can only belong to a single link aggregation group. A link
aggregation group may not cross an 8-port boundary, starting with port 1 (a group may not contain ports 8
and 9, for example) and all of the ports in the group must be members of the same VLAN. Further, the
aggregated links must all be of the same speed and should be configured as full duplex.
The configuration of the lowest numbered port in the group becomes the configuration for all of the ports in
the aggregation group. This port is called the Master Port of the group, and all configuration options –
including the VLAN configuration – that can be applied to the Master Port are applied to the entire link
aggregation group.
Load balancing is automatically applied to the ports in the aggregated group, and a link failure within the
group causes the network traffic to be directed to the remaining links in the group.
The Spanning Tree Protocol will treat a link aggregation group as a single link, on the Switch level. On the
port level, the STP will use the port parameters of the Master Port in the calculation of port cost and in
determining the state of the link aggregation group. If two redundant link aggregation groups are
configured on the Switch, STP will block one entire group – in the same way STP will block a single port
that has a redundant link.
To configure port trunking, click on the LACP hyperlink in the Configuration folder and then click Link
Aggregation:
To configure port trunk groups, click the Add button to add a new trunk group and then use the Port
Trunking Configuration window below to set up trunk groups. To change or delete a port trunk group,
click the Modify or Delete option in the Current Trunking Group Entries table pictured above.
Figure 4- 4. Port Trunking Group table
53
Page 54

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 5. Port Trunking Configuration menu
The user-changeable parameters are as follows:
Parameter Description
Group ID
State
Select an ID number for the group.
Trunk groups can be toggled between Enabled and Disabled. This is used
to turn a port trunking group on or off. This is useful for diagnostics, to
quickly isolate a bandwidth intensive network device or to have an
absolute backup aggregation group that is not under automatic control.
Type
This pull-down menu allows you to select between Static and LACP (Link
Aggregation Control Protocol.) LACP allows for the automatic detection of
links in a Port Trunking Group.
Master Port
Member Unit
Choose the Master port for the trunk group.
Choose the Switch unit on which to set up a trunk group. Trunk groups
must be confined to ports on a single Switch.
Port Map
Choose the members of the trunked group. Up to eight ports per group
can be assigned to a group.
Flooding Port
A trunking group must designate one port to allow transmission of
broadcasts and unknown unicasts.
Active Port
Shows the port that is currently forwarding packets.
54
Page 55
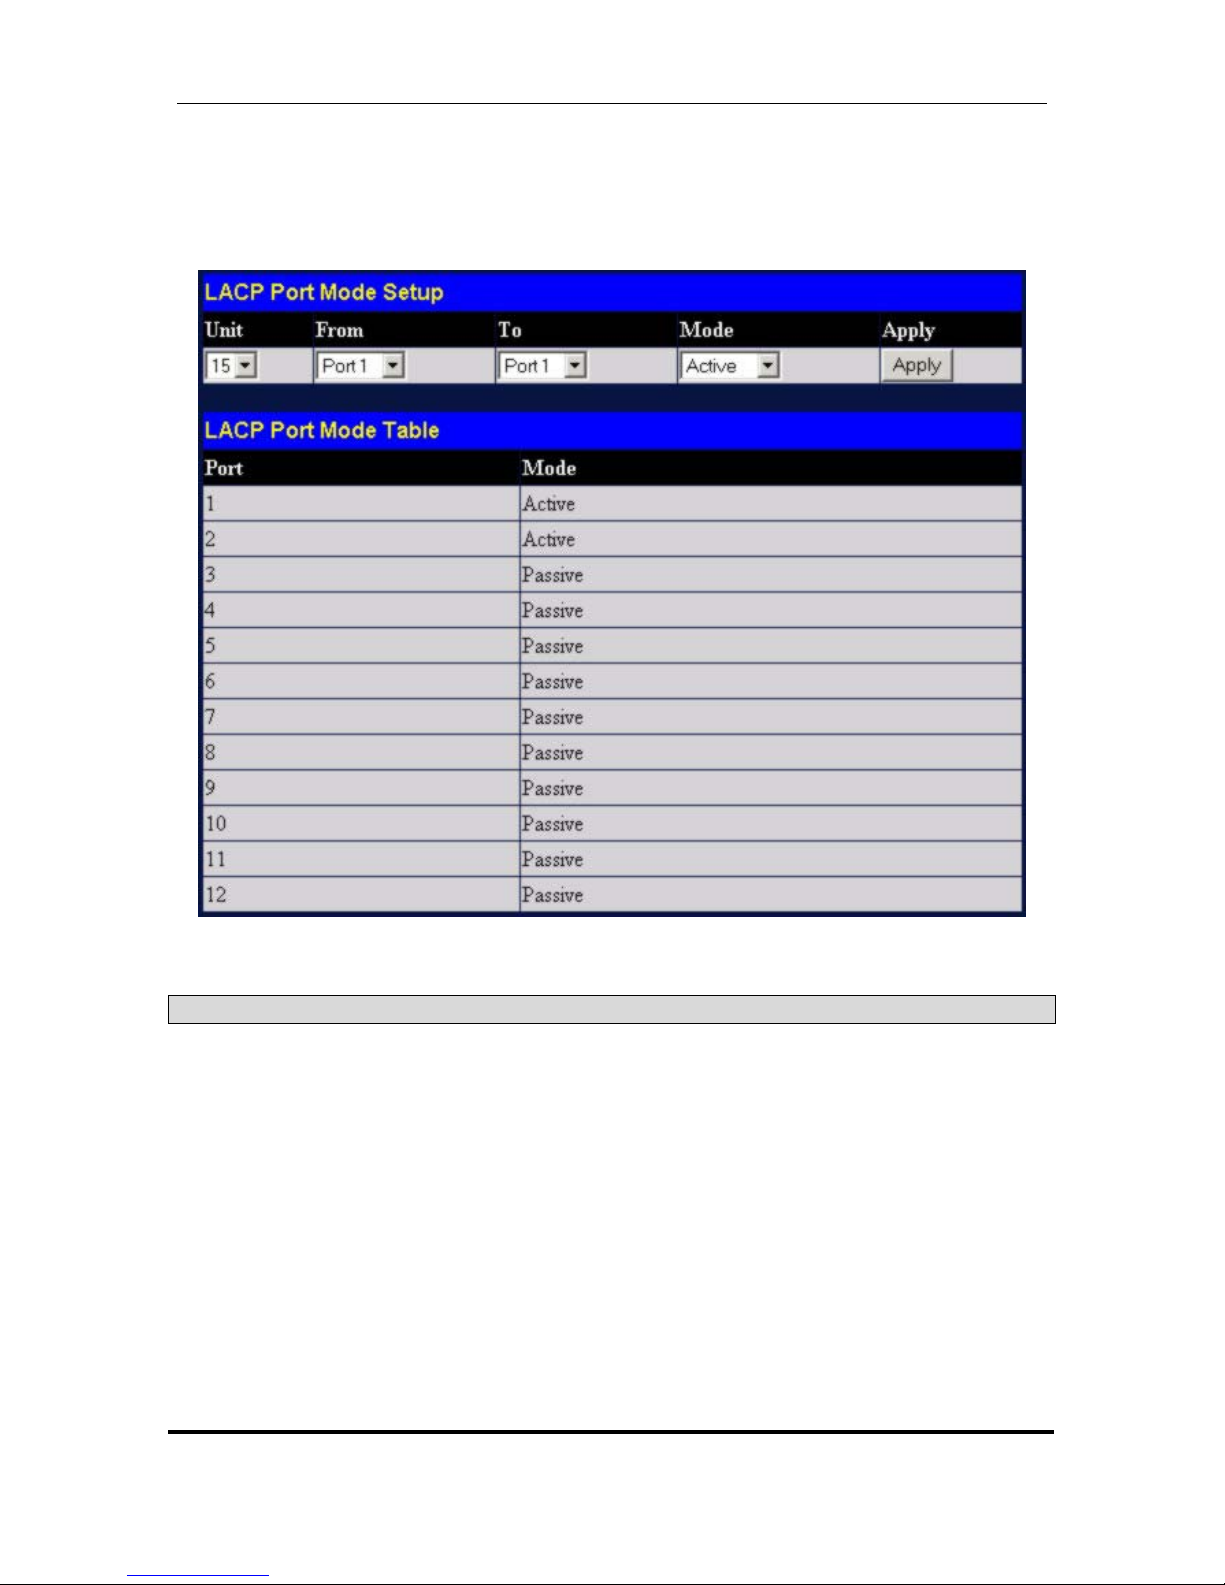
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
LACP Port Settings
The LACP Port Mode Setup window is used in conjunction with the Link Aggregation window to create
port trunking groups on the Switch. Using the following window, the user may set which ports will be
active and passive in processing and sending LACP control frames.
Figure 4- 6. LACP Port Mode Setup and Table
The user may set the following parameters:
Parameter Description
Unit
This is the Unit ID of a Switch in a Switch stack. The number 15
indicates a GSW-1290 Switch in standalone mode.
From/To
A consecutive group of ports may be configured starting with the
selected port.
Mode
Active – Active LACP ports are capable of processing and sending
LACP control frames. This allows LACP compliant devices to negotiate
the aggregated link so the group may be changed dynamically as needs
require. In order to utilize the ability to change an aggregated port group,
that is, to add or subtract ports from the group, at least one of the
participating devices must designate LACP ports as active. Both devices
must support LACP.
Passive – LACP ports that are designated as passive cannot initially
send LACP control frames. In order to allow the linked port group to
negotiate adjustments and make changes dynamically, at one end of the
55
Page 56
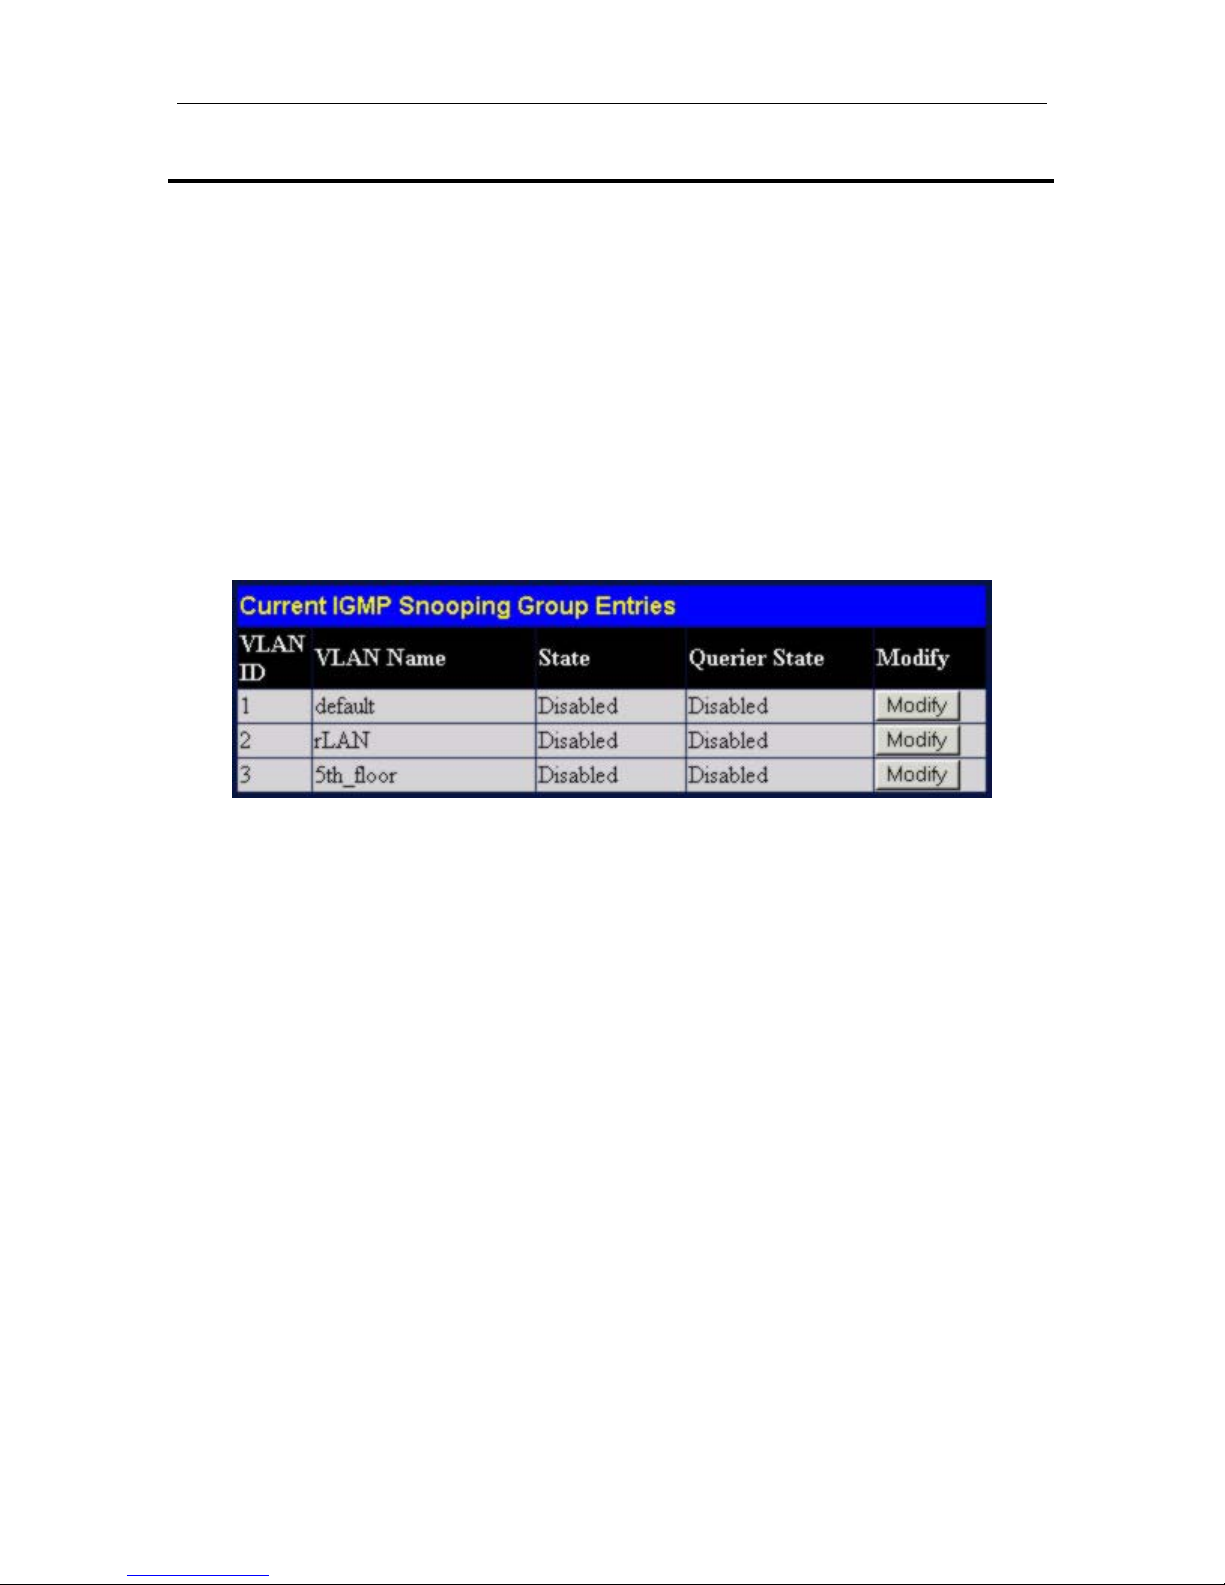
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
connection must have “active” LACP ports.
After setting the previous parameters, click Apply to allow your changes to be implemented. The LACP
Port Table shows which ports are active and/or passive.
IGMP
In order to use IGMP Snooping it must first be enabled for the entire Switch (see Advanced Settings). You
may then fine-tune the settings for each VLAN using the IGMP Snooping Settings window. When
enabled for IGMP snooping, the Switch can open or close a port to a specific Multicast group member
based on IGMP messages sent from the device to the IGMP host or vice versa. The Switch monitors IGMP
messages and discontinues forwarding multicast packets when there are no longer hosts requesting that
they continue.
IGMP Snooping
Use this window to view IGMP Snooping status. To modify settings, click the Modify button for the
VLAN ID you want to change.
Figure 4- 7. Current IGMP Snooping Group Entries table
Click the Modify button to bring up the IGMP Snooping Settings window pictured below.
56
Page 57
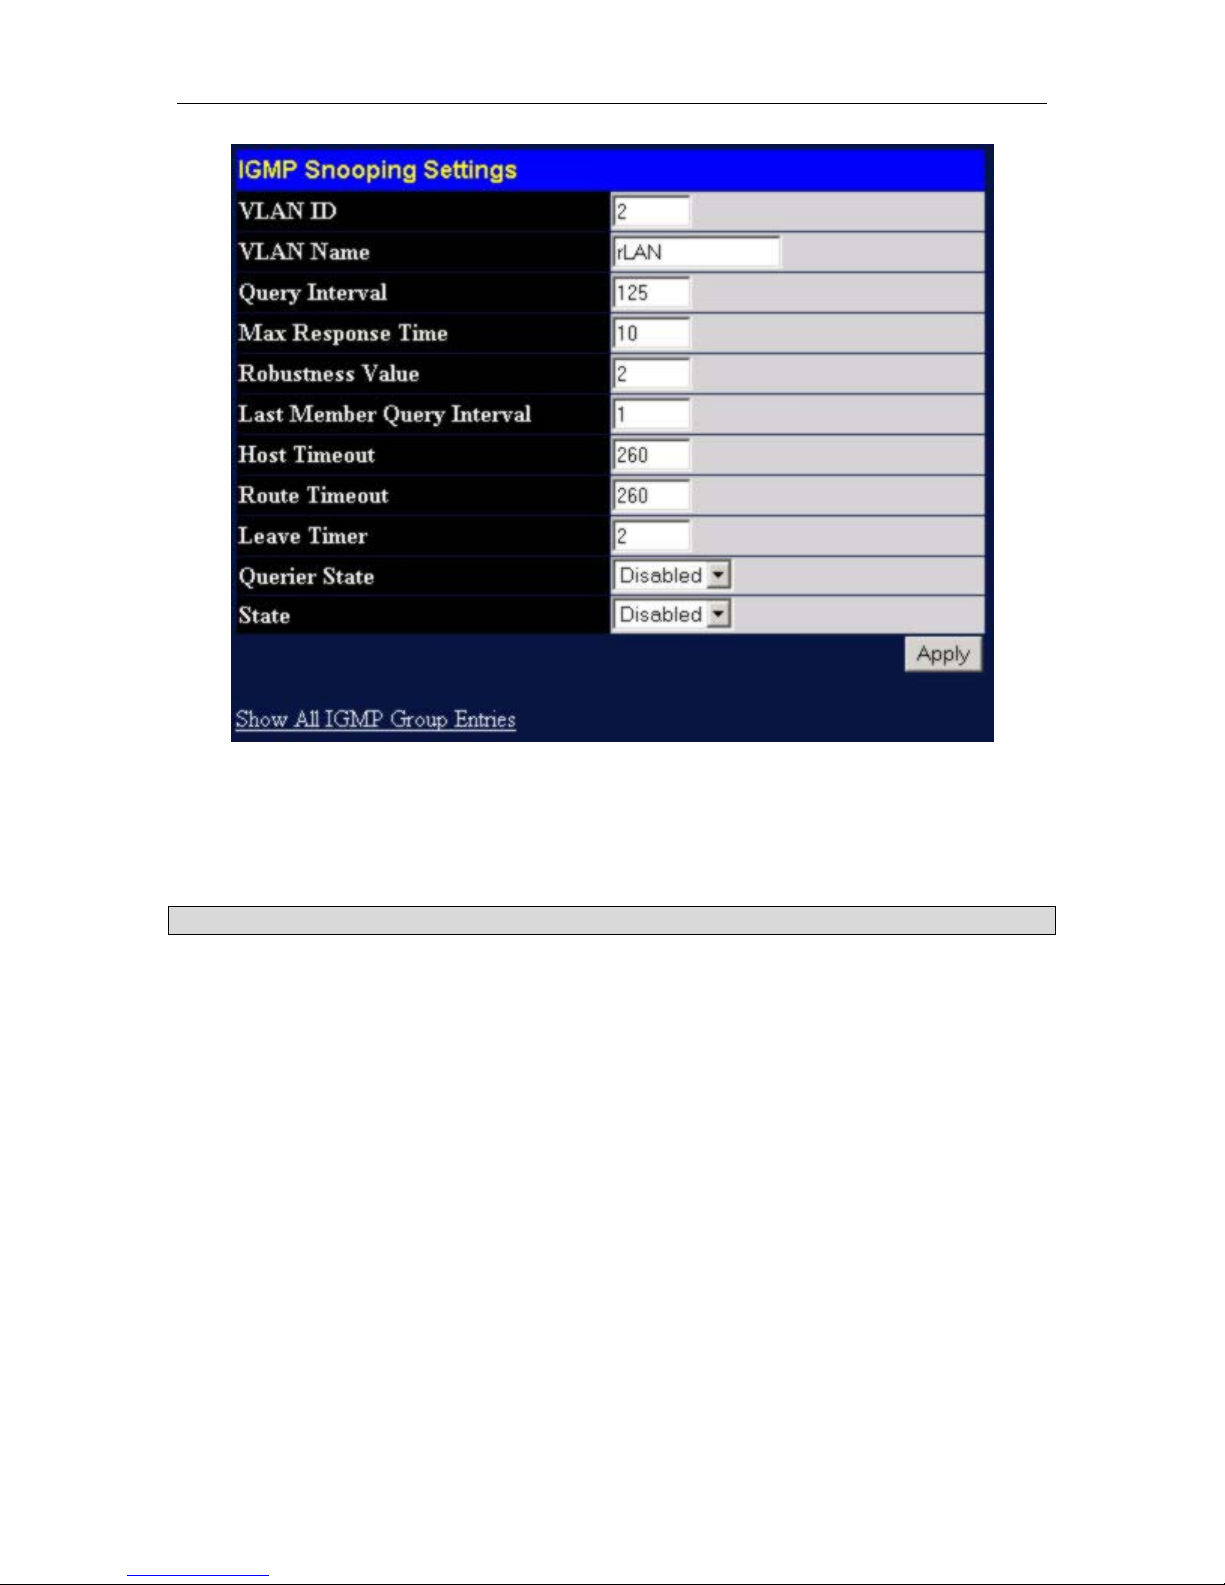
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 8. IGMP Snooping Settings menu
The IGMP Snooping Settings are described below:
Parameter Description
VLAN ID
VLAN Name
Query Interval
Max Response Time
Robustness Variable
The VLAN ID number.
The VLAN name.
The Query Interval field is used to set the time (in seconds) between
transmitting IGMP queries. Entries between 1 and 9,999 seconds are
allowed. The default value is 125.
This determines the maximum amount of time in seconds allowed before
sending an IGMP response report. The Max Response Time field allows
an entry between 1 and 25 (seconds). The default value is 10.
Adjust this variable according to expected packet loss. If packet loss on
the VLAN is expected to be high, the Robustness Variable should be
increased to accommodate increased packet loss. This entry field allows
an entry of 2 to 255. The default value is 2.
Last Member Query
Interval
Specifies the maximum amount of time between group-specific query
messages, including those sent in response to leave group messages.
The default value is 1.
57
Page 58
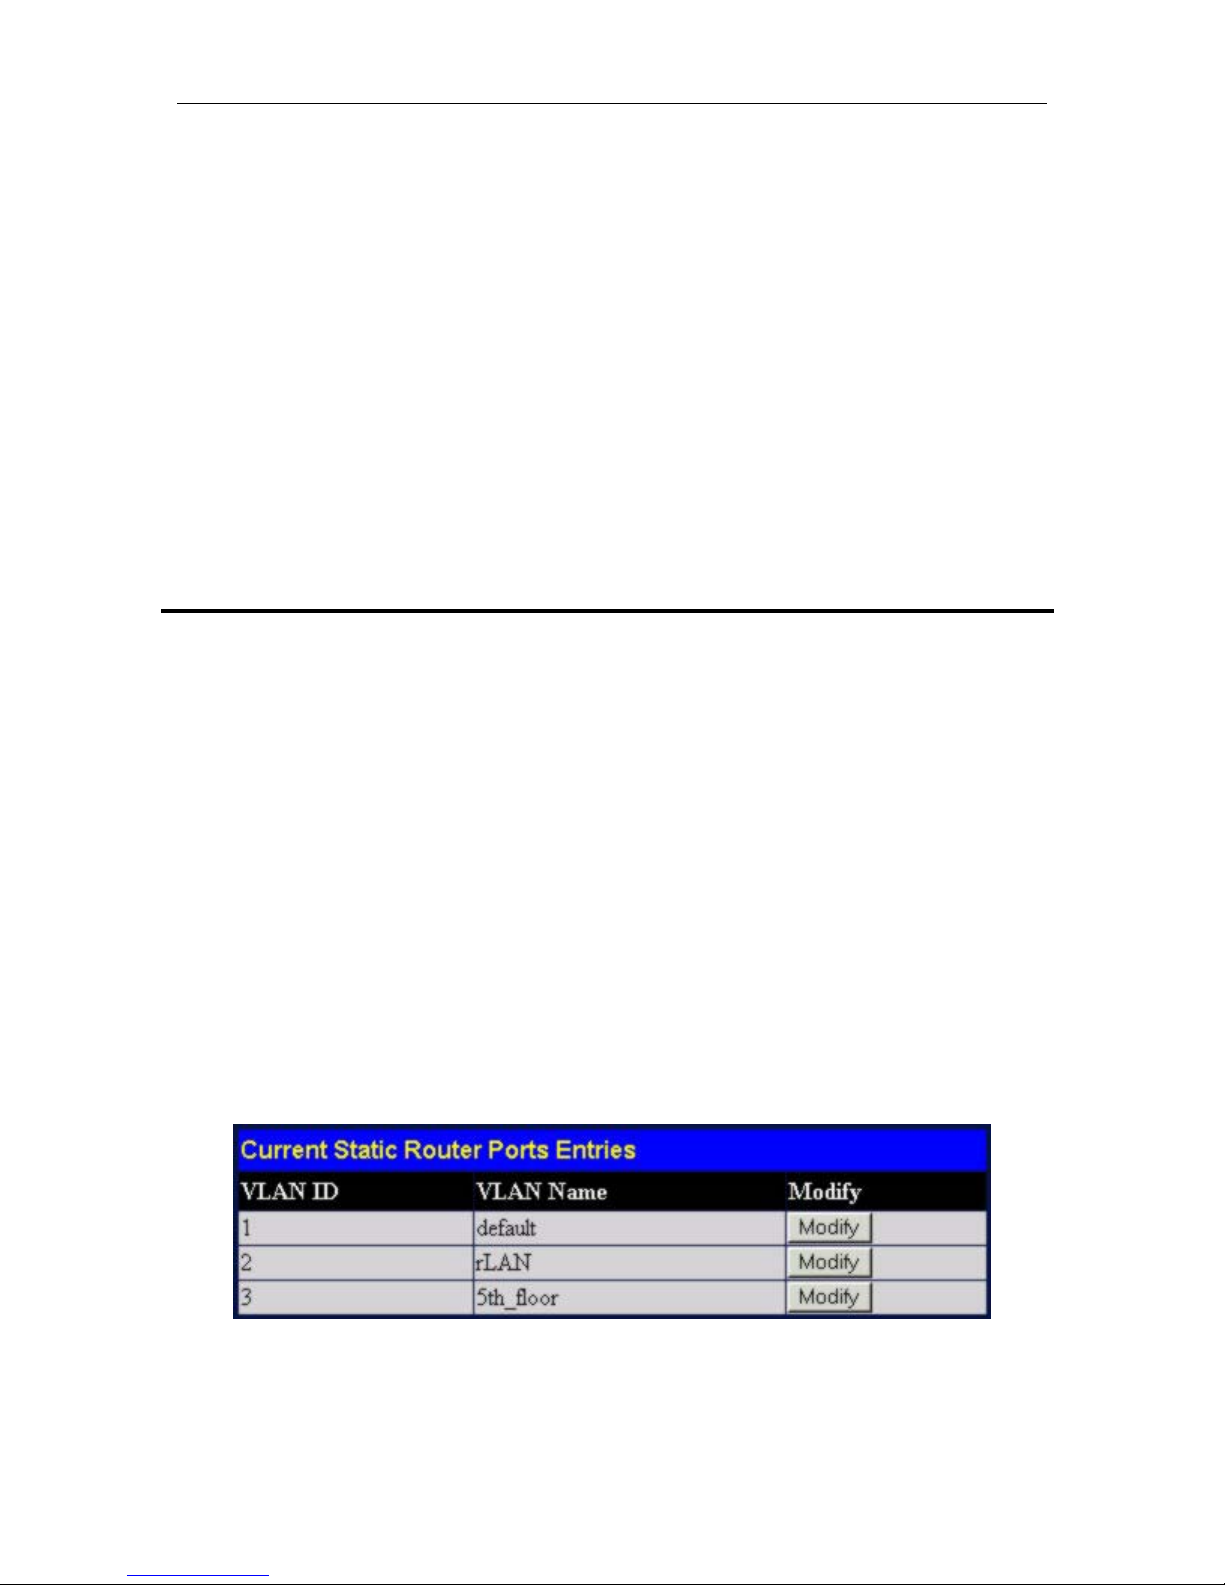
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Host Timeout
Route Timeout
Leave Timer
This is the maximum amount of time in seconds allowed for a host to
continue membership in a multicast group without the Switch receiving a
host membership report. The default value is 260.
This is the maximum amount of time in seconds a route is kept in the
forwarding table without receiving a membership report. The default
value is 260.
This specifies the maximum amount of time in seconds between the
Switch receiving a leave group message from a host, and the Switch
issuing a group membership query. If no response to the membership
query is received before the Leave Timer expires, the (multicast)
forwarding entry for that host is deleted.
Querier State
Choose Enabled to enable transmitting IGMP Query packets. The
default value is Disabled.
State
Select Enabled to implement IGMP Snooping. This is Disabled by
default.
Static Router Ports Entry
A static router port is a port that has a multicast router attached to it. Generally, this router would have a
connection to a WAN or to the Internet. Establishing a router port will allow multicast packets coming
from the router to be propagated through the network, as well as allowing multicast messages (IGMP)
coming from the network to be propagated to the router.
A router port has the following behavior characteristics:
• All IGMP Report packets will be forwarded to the router port.
• IGMP queries (from the router port) will be flooded to all ports.
All UDP multicast packets will be forwarded to the router port. Because routers do not send IGMP reports
or implement IGMP snooping, a multicast router connected to the router port of the Layer 3 Switch would
not be able to receive UDP data streams unless the UDP multicast packets were all forwarded to the router
port.
A router port will be dynamically configured when IGMP query packets, RIPv2 multicast, DVMRP
multicast, and PIM-DM multicast packets are detected flowing into a port.
Open the IGMP folder and the click on the Static Router Ports Entry link to open the Current Static
Router Ports Entries window, as shown below.
Figure 4- 9. Current Static Router Port Entries table
The window displays all of the current entries to the Switch’s static router port table. To add or modify an
entry, click the Modify button. This will open the Static Router Ports Settings window, as shown below.
58
Page 59

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 10. Static Router Ports Settings menu
To configure a static router port(s):
1. Select the Unit containing the static router port.
2. Select the Port or Ports that will become static router ports.
3. Click Apply to let the changes take effect.
The following parameters are listed in the Static Router Port windows.
Parameter Description
VLAN ID (VID)
VLAN Name
Unit
Member Ports
This is the VLAN ID that, along with the VLAN name, identifies the VLAN
where the multicast router is attached.
This is the name of the VLAN where the multicast router is attached.
This is the Unit ID of the Switch in a Switch stack for which you are
creating an entry into the Switch’s static router port table.
There are the ports on the Switch that will have a multicast router attached
to them.
Spanning Tree
The Switch supports 802.1d Spanning Tree Protocol (STP) and 802.1w Rapid Spanning Tree Protocol
(RSTP). 802.1d STP will be familiar to most networking professionals. However since 802.1w RSTP has
been recently introduced to LevelOne managed Ethernet Switches, a brief introduction to the technology is
provided below followed by a description of how to set up 802.1 d STP and 802.1w RSTP.
802.1w Rapid Spanning Tree
The Switch implements two versions of the Spanning Tree Protocol, the Rapid Spanning Tree Protocol
(RSTP) as defined by the IEE 802.1w specification and a version compatible with the IEEE 802.1d STP.
RSTP can operate with legacy equipment implementing IEEE 802.1d, however the advantages of using
RSTP will be lost.
The IEEE 802.1w Rapid Spanning Tree Protocol (RSTP) evolved from the 802.1d STP standard. RSTP
was developed in order to overcome some limitations of STP that impede the function of some recent
Switching innovations, in particular, certain Layer 3 function that are increasingly handled by Ethernet
Switches. The basic function and much of the terminology is the same as STP. Most of the settings
59
Page 60
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
configured for STP are also used for RSTP. This section introduces some new Spanning Tree concepts and
illustrates the main differences between the two protocols.
Port Transition States
An essential difference between the two protocols is in the way ports transition to a forwarding state and
the in the way this transition relates to the role of the port (forwarding or not forwarding) in the topology.
RSTP combines the transition states disabled, blocking and listening used in 802.1d and creates a single
state Discarding. In either case, ports do not forward packets; in the STP port transition states disabled,
blocking or listening or in the RSTP port state discarding there is no functional difference, the port is not
active in the network topology. The Comparing Port States table below compares how the two protocols
differ regarding the port state transition.
Both protocols calculate a stable topology in the same way. Every segment will have a single path to the
root bridge. All bridges listen for BPDU packets. However, BPDU packets are sent more frequently – with
every Hello packet. BPDU packets are sent even if a BPDU packet was not received. Therefore, all links
between bridges are sensitive to the status of the link. Ultimately this difference results faster detection of
failed links, and thus faster topology adjustment. A drawback of 802.1d is this absence of immediate
feedback from adjacent bridges.
802.1d STP 802.1w RSTP Forwarding? Learning?
Disabled Discarding No No
Blocking Discarding No No
Listening Discarding No No
Learning Learning No Yes
Forwarding Forwarding Yes Yes
Table 4- 1. Comparing Port States
RSTP is capable of more rapid transition to a forwarding state – it no longer relies on timer
configurations – RSTP compliant bridges are sensitive to feedback from other RSTP compliant bridge links.
Ports do not need to wait for the topology to stabilize before transitioning to a forwarding state. In order to
allow this rapid transition, the protocol introduces two new variables: the edge port and the point-to-point
(P2P) port.
Edge Port
The edge port is a configurable designation used for a port that is directly connected to a segment where a
loop cannot be created. An example would be a port connected directly to a single workstation. Ports that
are designated as edge ports will transition to a forwarding state immediately without going through the
listening and learning states. An edge port loses its status if it receives a BPDU packet, immediately
becoming a normal spanning tree port.
P2P Port
A P2P port is also capable of rapid transition. P2P ports may be used to connect to other bridges. Under
RSTP, all ports operating in full-duplex mode are considered to be P2P ports, unless manually overridden
through configuration.
802.1d/802.1w Compatibility
RSTP can interoperate with legacy equipment and is capable of automatically adjusting BPDU packets to
802.1d format when necessary. However, any segment using 802.1 STP will not benefit from the rapid
transition and rapid topology change detection of RSTP. The protocol also provides for a variable used for
migration in the event that legacy equipment on a segment is updated to use RSTP.
Switch Spanning Tree Settings
The Spanning Tree Protocol (STP) operates on two levels: on the Switch level, the settings are globally
implemented. On the port level, the settings are implemented on a per user-defined group of ports basis.
60
Page 61
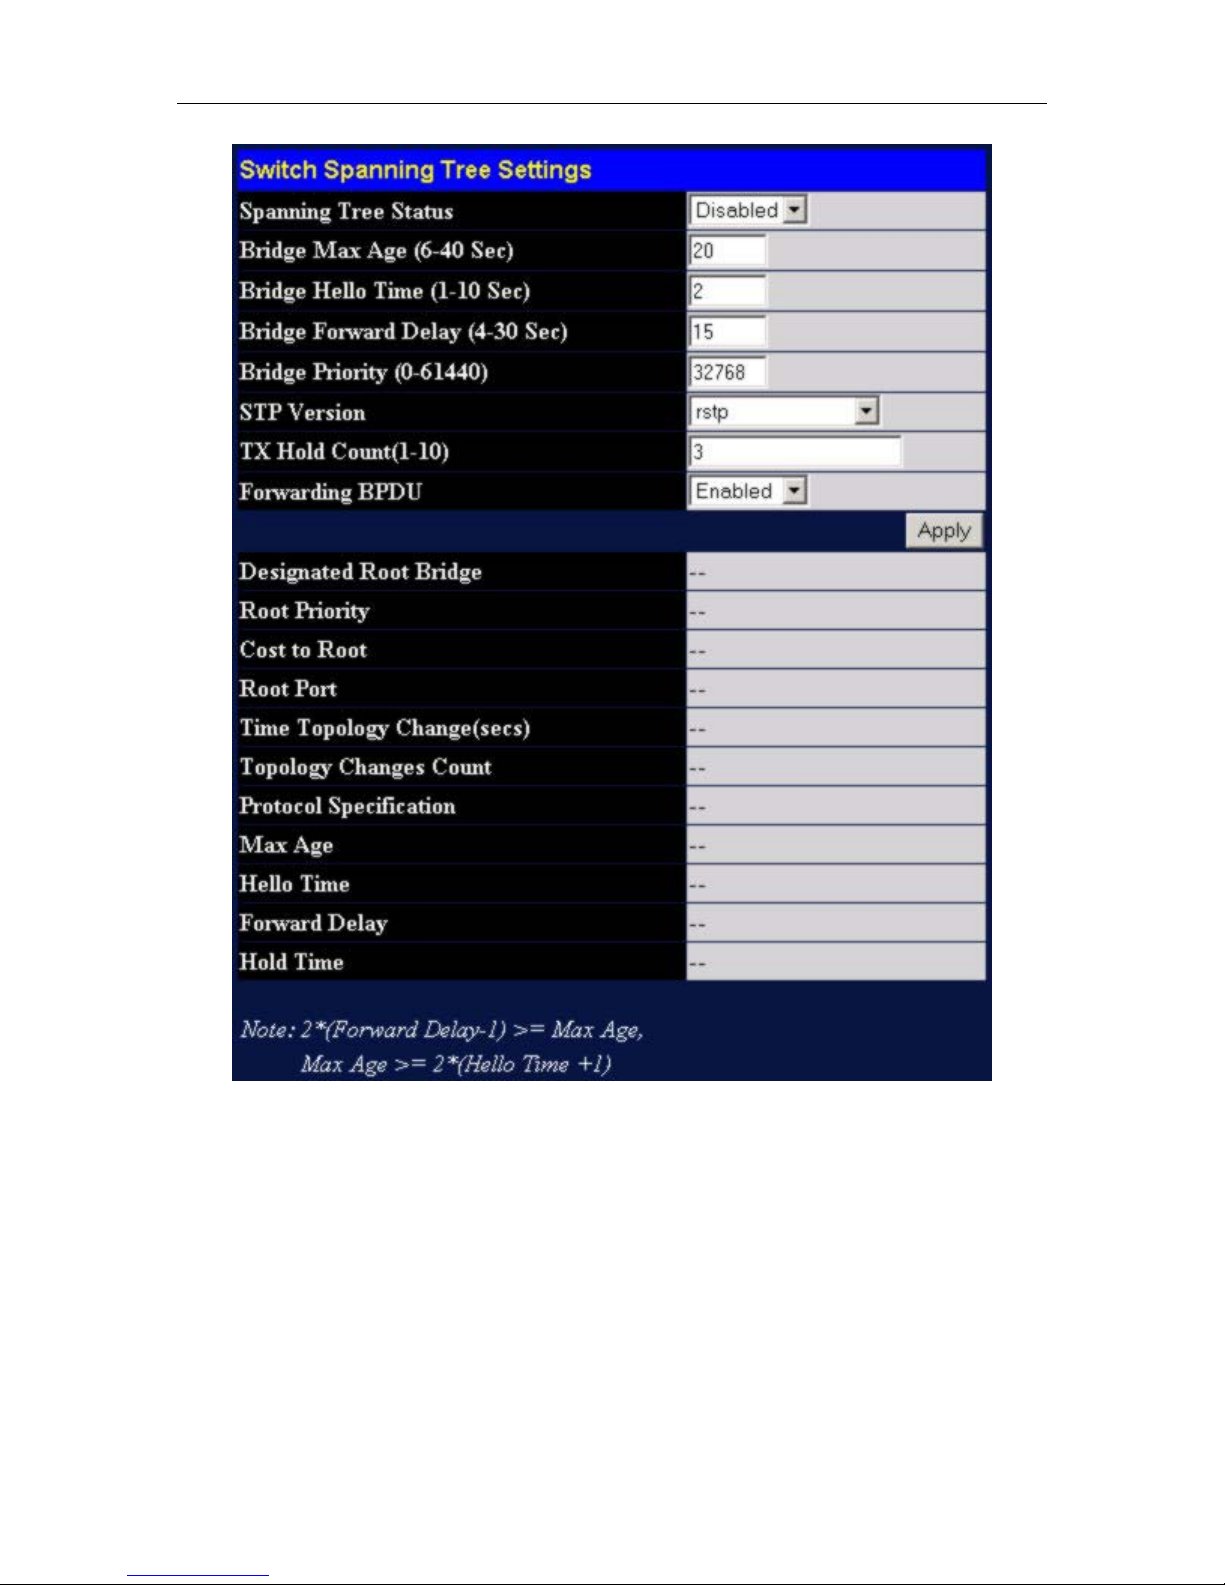
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 11. Switch Spanning Tree Settings menu
61
Page 62
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Configure the following system-wide STP parameters and click the Apply button to implement them:
Parameter Description
Spanning Tree
Status <Disabled>
This field can be toggled between Enabled and Disabled using the pulldown menu. This will enable or disable the Spanning Tree Protocol
(STP), globally, for the Switch.
Bridge Max Age (6 40 sec) <20 >
The Max. Age can be set from 6 to 40 seconds. At the end of the Max.
Age, if a BPDU has still not been received from the Root Bridge, your
Switch will start sending its own BPDU to all other Switches for
permission to become the Root Bridge. If it turns out that your Switch has
the lowest Bridge Identifier, it will become the Root Bridge.
Bridge Hello Time (1
- 10 sec) < 2 >
The Hello Time can be set from 1 to 10 seconds. This is the interval
between two transmissions of BPDU packets sent by the Root Bridge to
tell all other Switches that it is indeed the Root Bridge.
Bridge Forward
Delay (4 - 30 sec)
<15 >
Bridge Priority (0 -
61440) <32768>
The Forward Delay can be from 4 to 30 seconds. This is the time any port
on the Switch spends in the listening state while moving from the blocking
state to the forwarding state.
A Priority for the Switch can be set from 0 to 61440. This number is used
in the voting process between Switches on the network to determine
which Switch will be the root Switch. A low number indicates a high
priority, and a high probability that this Switch will be elected as the root
Switch.
STP Version<rstp > Choose rstp (default) or Stp Compatibility. Both versions use STP
parameters in the same way. RSTP is fully compatible with IEEE 802.1d
STP and will function with legacy equipment.
Tx Hold Count(1-10)
<3 >
Forwarding BPDU
<Enabled >
This is the maximum number of Hello packets transmitted per interval.
The count can be specified from 1 to 10. The default value is 3.
This can be Enabled or Disabled. When it is Enabled it allows the
forwarding of STP BPDU packets from other network devices when STP
is disabled on the Switch. The default is Enabled.
NOTE: The Hello Time cannot be longer than the Max. Age. Otherwise, a
configuration error will occur
.
Observe the following formulas when setting the above parameters:
Max. Age = 2 x (Forward Delay - 1 second)
Max. Age = 2 x (Hello Time + 1 second)
62
Page 63
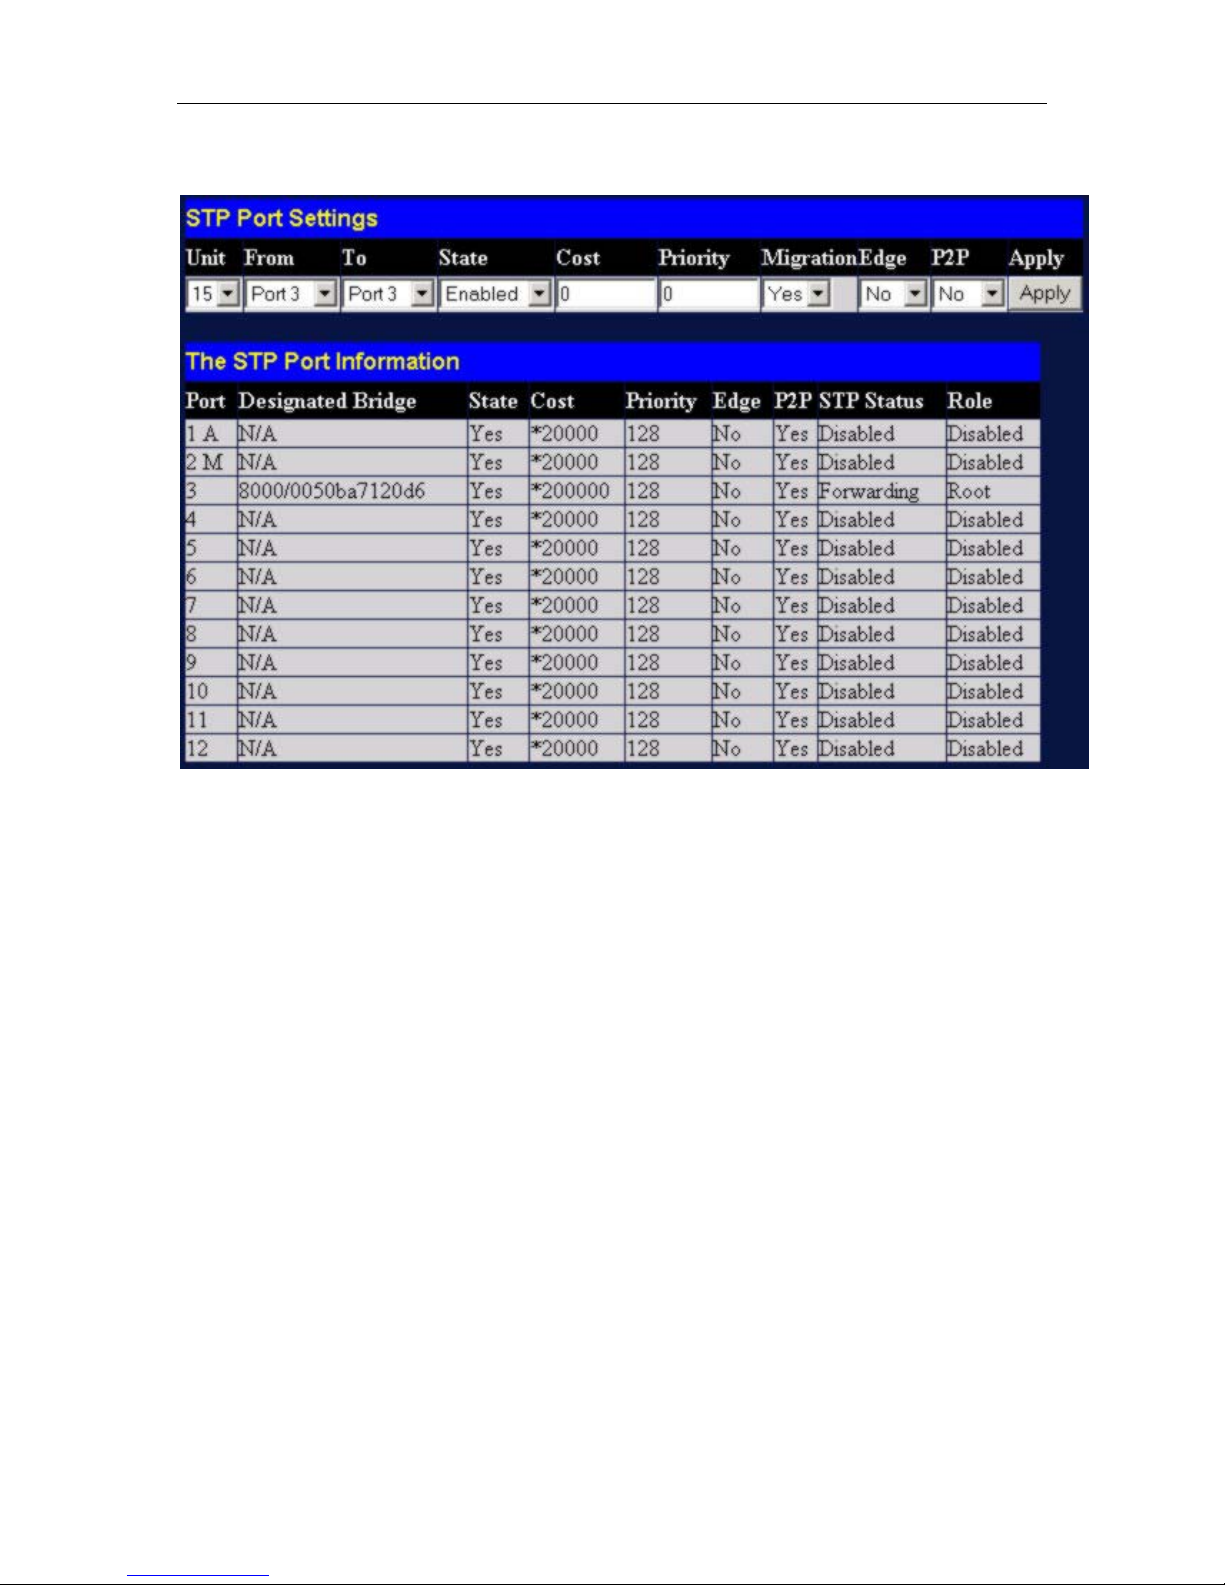
STP Port Settings
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 12. STP Port Settings and Information menu
In addition to setting Spanning Tree parameters for use on the Switch level, the Switch allows for the
configuration of groups of ports, each port-group of which will have its own spanning tree, and will require
some of its own configuration settings. An STP Group will use the Switch-level parameters entered above,
with the addition of Port Priority and Port Cost.
An STP Group spanning tree works in the same way as the Switch-level spanning tree, but the root bridge
concept is replaced with a root port concept. A root port is a port of the group that is elected on the basis of
port priority and port cost, to be the connection to the network for the group. Redundant links will be
blocked, just as redundant links are blocked on the Switch level.
The STP on the Switch level blocks redundant links between Switches (and similar network devices). The
port level STP will block redundant links within an STP Group.
It is advisable to define an STP Group to correspond to a VLAN group of ports.
63
Page 64
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The following fields can be set for STP port configuration:
Parameter Description
Unit
From/To
State
Cost
Priority
Migration
This is the Unit ID of a Switch in a Switch stack. The number 15 indicates
a GSW-1290 Switch in standalone mode.
A consecutive group of ports may be configured starting with the selected
port.
This drop-down menu allows you to enable or disable STP for the
selected group of ports.
A Port Cost can be set from 1 to 200000000. The lower the number, the
greater the probability the port will be chosen to forward packets.
Default port cost:
100Mbps port = 200000
Gigabit ports = 20000
A Port Priority can be from 0 to 240. The lower the number, the greater
the probability the port will be chosen as the Root Port.
Select Yes or No. Choosing Yes will enable the port to migrate from
802.1d STP status to 802.1w RSTP status. RSTP can coexist with
standard STP, however the benefits of RSTP are not realized on a port
where an 802.1d network connects to an 802.1w enabled network.
Migration should be enabled (Yes) on ports connected to network stations
or segments that will be upgraded to 802.1w RSTP on all or some portion
of the segment.
Edge
P2P
Select Yes or No. Choosing Yes designates the port as an edge port.
Edge ports cannot create loops, however an edge port can lose edge port
status if a topology change creates a potential for a loop. An edge port
normally should not receive BPDU packets. If a BPDU packet is received
it automatically loses edge port status. No indicates the port does not
have edge port status.
Select Yes or No. Choosing Yes indicates a point-to-point (p2p) shared
link. These are similar to edge ports however they are restricted in that a
p2p port must operate in full duplex. Like edge ports, p2p ports transition
to a forwarding state rapidly thus benefiting from RSTP.
64
Page 65
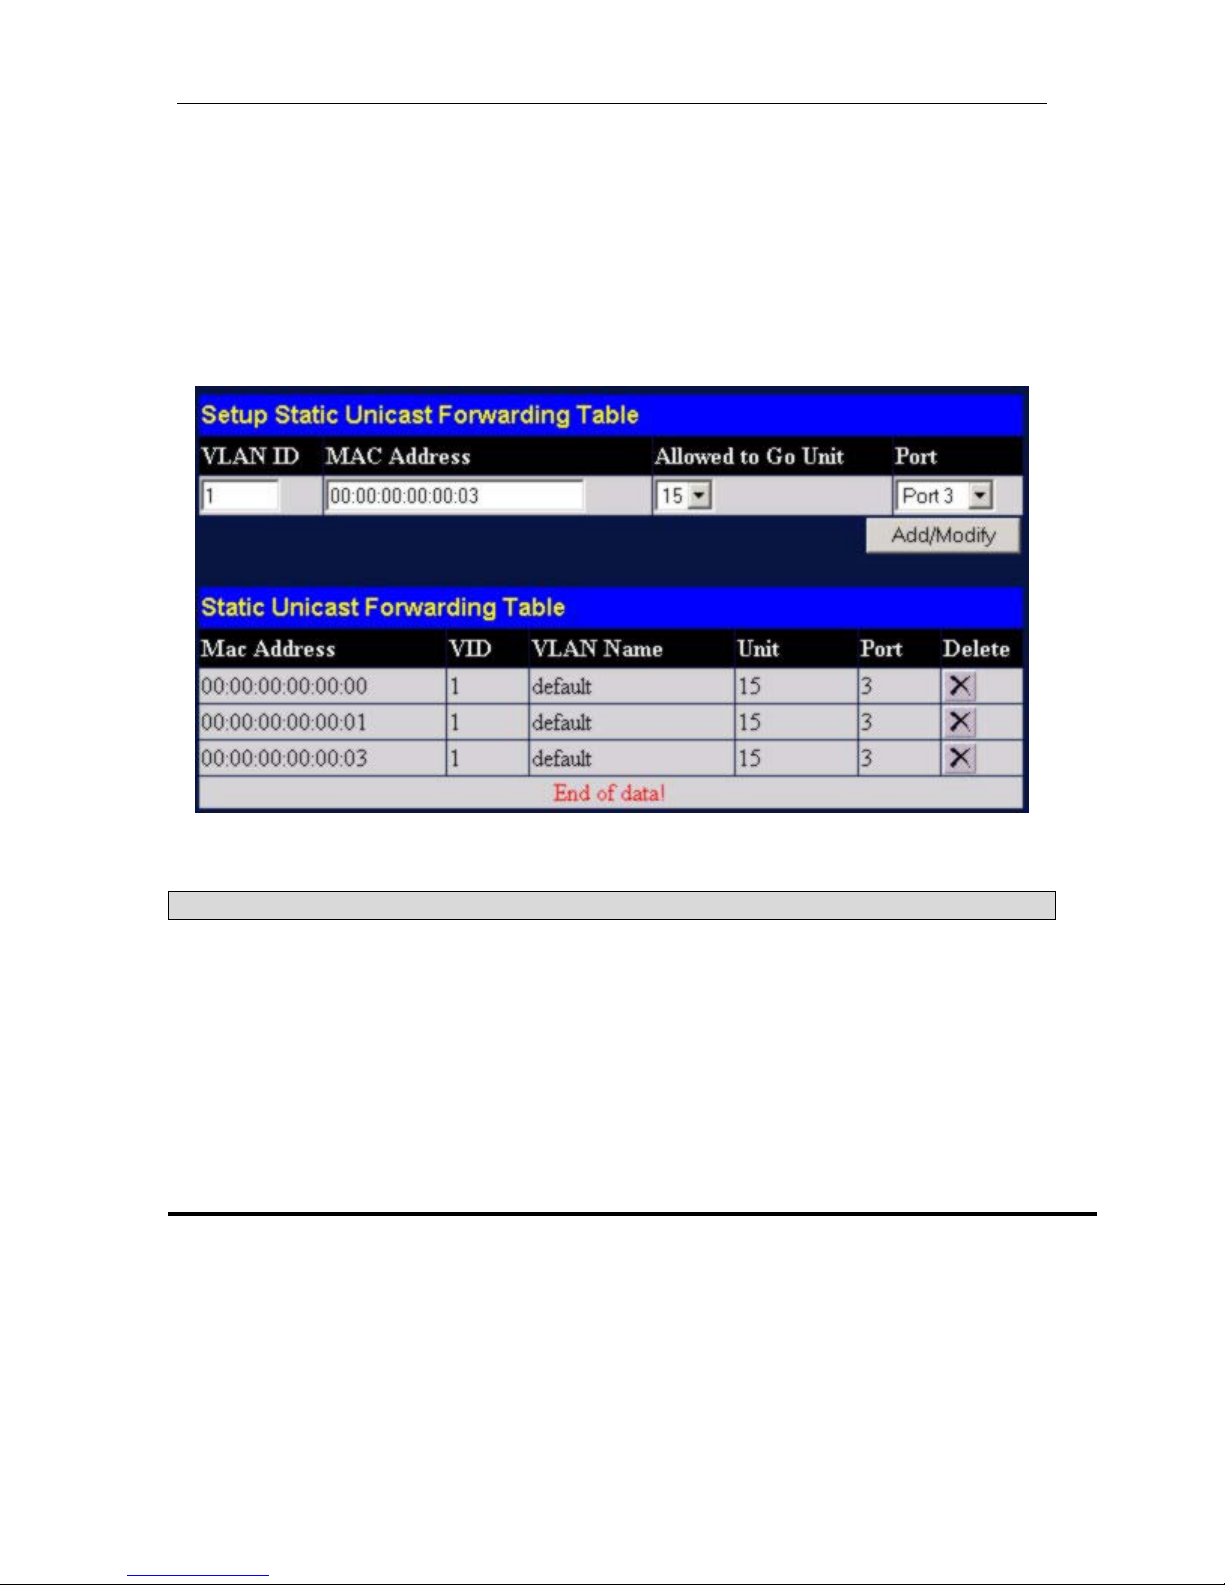
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Forwarding & Filtering
The Switch allows permanent or static entries into the forwarding database (FDB). These FDB entries are
MAC addresses that will not age out. In addition, multicast forwarding may be customized to conform to
rules for the different ports by setting up multicast filter modes for each port.
Unicast Forwarding
Open the Forwarding & Filtering folder and click on the Unicast Forwarding link. This will open the
Setup Static Unicast Forwarding Table window, as shown below.
Figure 4- 13. Setup Static Unicast Forwarding Setup and table
To add an entry, define the following parameters:
Parameter Description
VLAN ID
MAC Address
Allowed to Go to
Unit
Port
Click on the Add/Modify button to add a unicast MAC address to the Switch’s forwarding table, or to
modify a previous entry.
The VLAN ID number of the VLAN on which the above Unicast MAC address
resides.
The MAC address to which packets will be statically forwarded. This must be
a unicast MAC address.
Allows the designation of the module on which the above MAC address
resides.
Choose the port on which the MAC address resides. Selecting Port 0 means
no ports are allowed.
65
Page 66
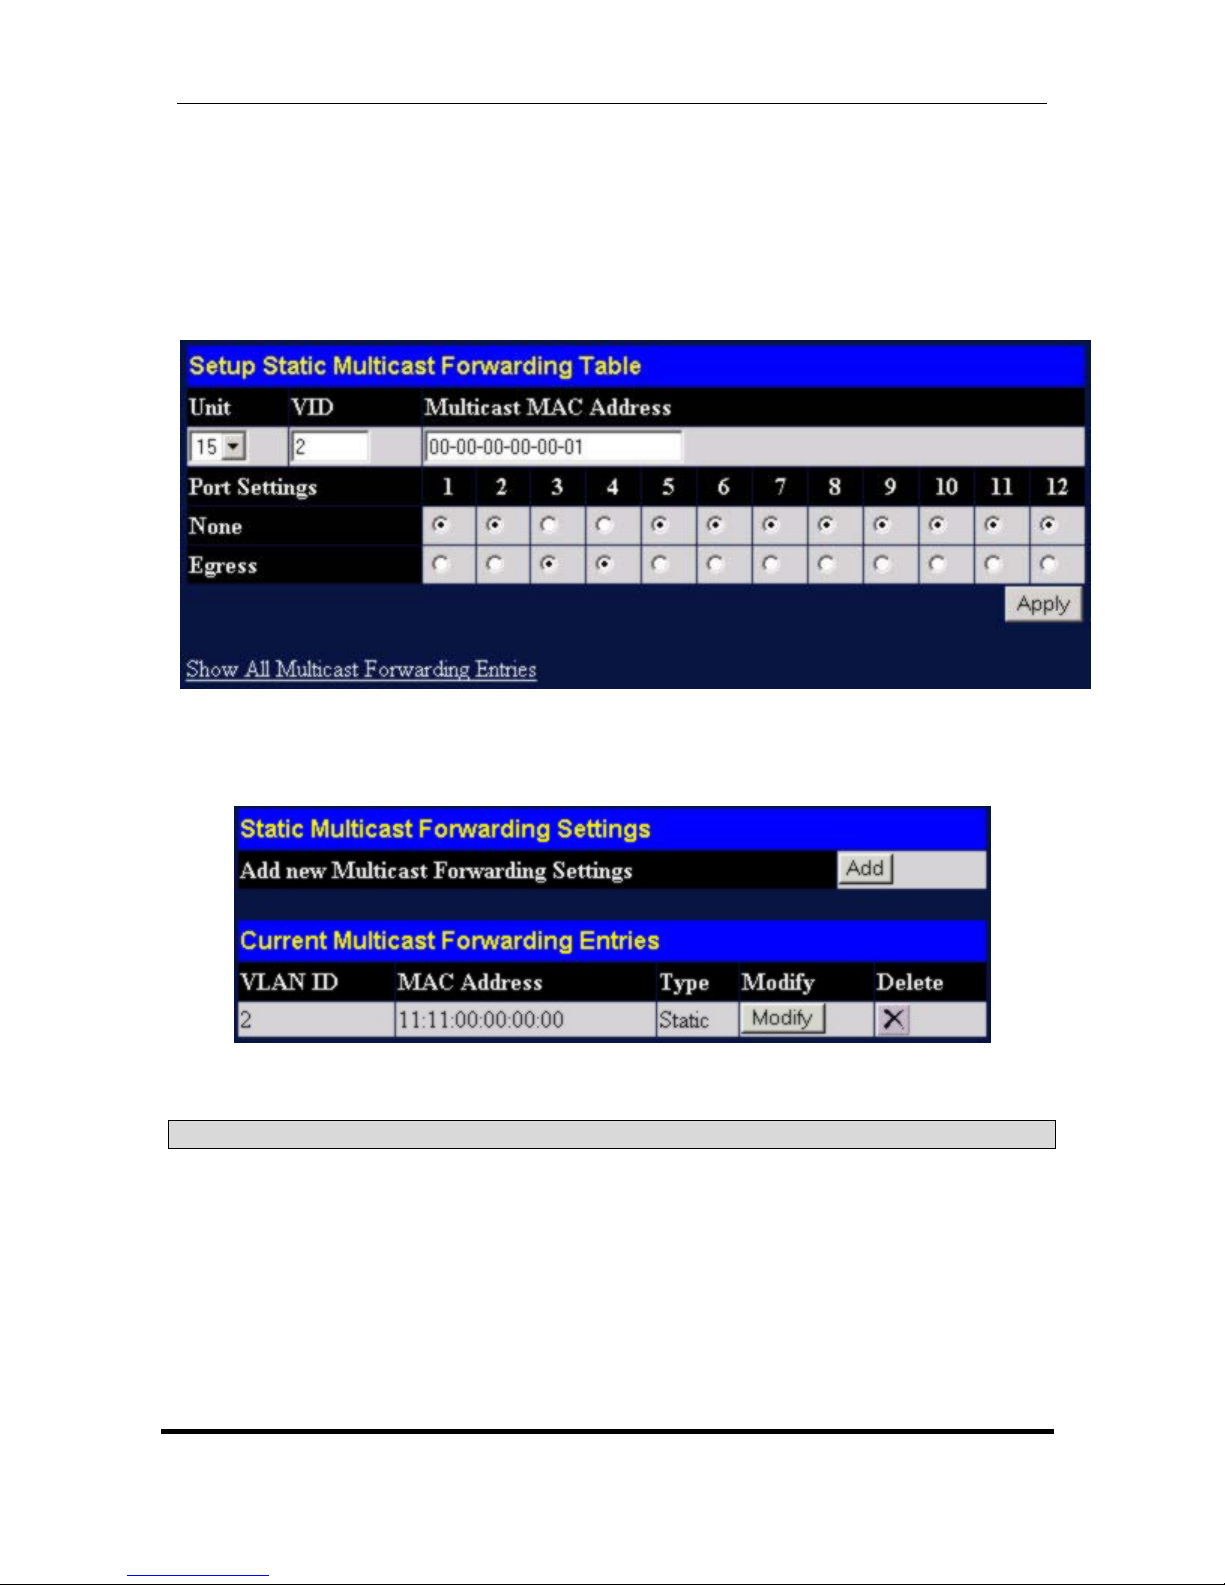
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Multicast Forwarding
The following window describes how to set up Multicast forwarding on the Switch. Open the Forwarding
& Filtering folder and click on the Multicast Forwarding link to see the entry window below:
Figure 4- 14. Static Multicast Forwarding Settings menu
The Static Multicast Forwarding Settings window displays all of the entries made into the Switch’s static
multicast forwarding table. Click the Add button to open the Setup Static Multicast Forwarding Table
window, as shown below.
Figure 4- 15. Setup Static Multicast Forwarding table
The following parameters can be set:
Parameter Description
Unit
This is the Unit ID of a Switch in a Switch stack. The number 15 indicates
a GSW-1290 Switch in standalone mode.
VID
The VLAN ID of the VLAN the MAC address below belongs to.
Multicast MAC
Address
Port Settings
The MAC address of the static source of multicast packets. This must be
a multicast MAC address.
Allows the selection of ports that will be members of the static multicast
group and ports that are either forbidden from joining dynamically, or that
can join the multicast group dynamically, using GMRP. The options are
66
Page 67
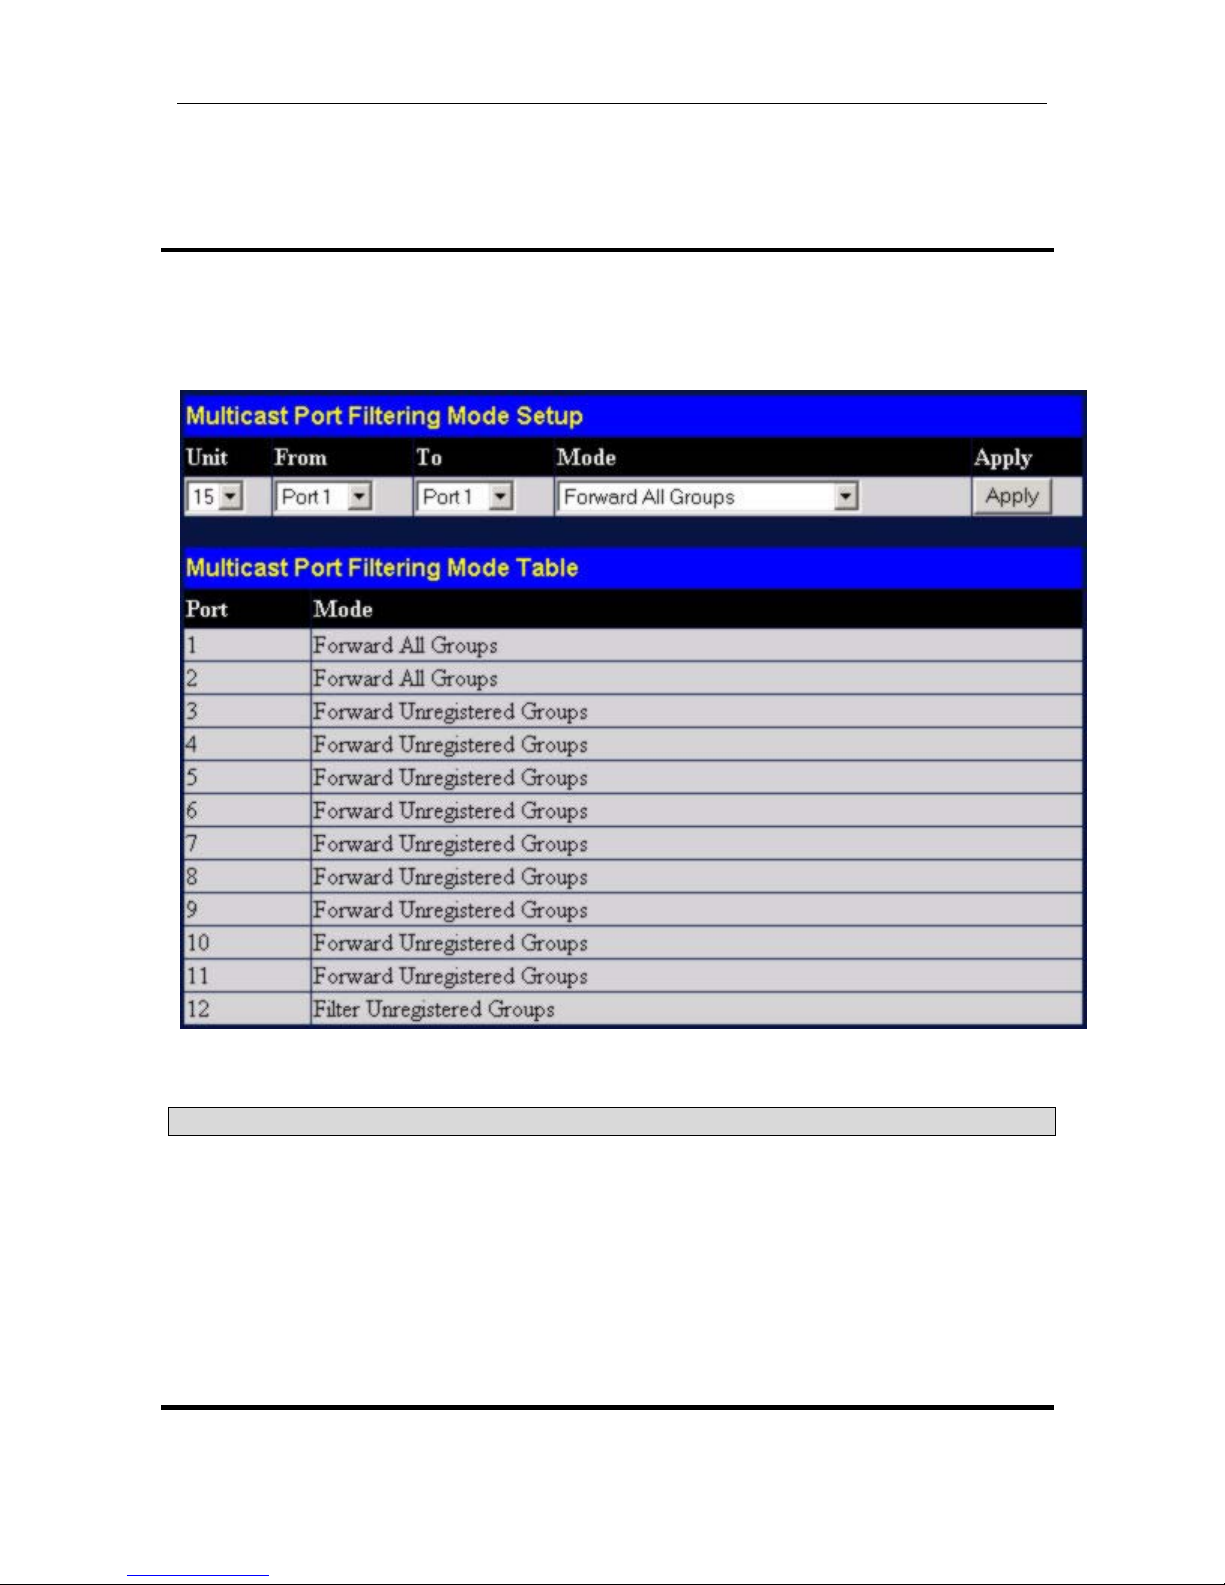
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
None and Egress. None means there are no restrictions on the port
dynamically joining the multicast group. If None is chosen, then an end
station attached to the port can join the multicast group using GMRP.
Egress means the port is a static member of the multicast group.
Multicast Port Filtering Mode
The following window describes how to set up Multicast port filtering on the Switch. Open the
Forwarding & Filtering folder and click on the Multicast Port Filtering Mode link to see the entry
window below:
Figure 4- 16. Multicast Port Filtering Mode Setup and table
The following parameters can be set:
Parameter Description
Unit
This is the Unit ID of a Switch in a Switch stack. The number 15 indicates
a GSW-1290 Switch in standalone mode.
From/To
A consecutive group of ports may be configured starting with the selected
port.
Mode
This drop-down menu allows you to select the action the switch will take
when it receives a multicast packet that is to be forwarded to one of the
ports in the range specified above.
Forward All Groups − Instructs the switch to forward a multicast packet to
67
Page 68
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
all multicast groups residing within the range of ports specified above.
Forward Unregistered Groups − Instructs the switch to forward a multicast
packet whose destination is an unregistered multicast group residing
within the range of ports specified above.
Filter Unregistered Groups − Instructs the switch to filter any multicast
packets whose destination is an unregistered multicast group residing
within the range of ports specified above
VLANs
The Switch Web Manager’s VLANs sub-folder is divided into two main windows, 802.1Q Static VLANs
and 802.1Q Port Settings. Each is described after a short overview of VLANs.
Understanding 802.1Q VLANs
This review of 802.1Q VLANs presents some basic background about how VLANs work according to the
IEEE 802.1Q standard. VLANs operate according to the same rules regardless of whether the Switching
environment is Layer 2 or Layer 3. The difference is primarily that in a Layer 3 Switch there is an added
capability of unique association between a VLAN and an IP interface or subnet group.
A VLAN is a collection of end nodes grouped by logic rather than physical location. End nodes that
frequently communicate with each other are assigned to the same VLAN, regardless of where they are
located physically on the network. Logically, a VLAN can be equated to a broadcast domain, because
broadcast packets are forwarded only to members of the VLAN on which the broadcast was initiated.
IEEE 802.1Q VLANs
Some relevant terms:
Tagging - The act of putting 802.1Q VLAN information into the header of a packet.
Untagging - The act of stripping 802.1Q VLAN information out of the packet header.
Ingress port - A port on a Switch where packets are flowing into the Switch and VLAN decisions must be
made.
Egress port - A port on a Switch where packets are flowing out of the Switch, either to another Switch or to
an end station, and tagging decisions must be made.
IEEE 802.1Q (tagged) VLANs are implemented on the GSW-1290 Switch. 802.1Q VLANs require tagging,
which enables the VLANs to span an entire network (assuming all Switches on the network are IEEE
802.1Q-compliant).
Any port can be configured as either tagging or untagging. The untagging feature of IEEE 802.1Q VLANs
allow VLANs to work with legacy Switches that don’t recognize VLAN tags in packet headers. The
tagging feature allows VLANs to span multiple 802.1Q VLAN compliant Switches through a single
physical connection and allows Spanning Tree to be enabled on all ports and work normally.
802.1Q VLAN Packet Forwarding
Packet forwarding decisions are made based upon the following three types of rules:
Ingress rules – rules relevant to the classification of received frames belonging to a VLAN.
Forwarding rules between ports – decides filter or forward the packet
Egress rules – determines if the packet must be sent tagged or untagged.
68
Page 69
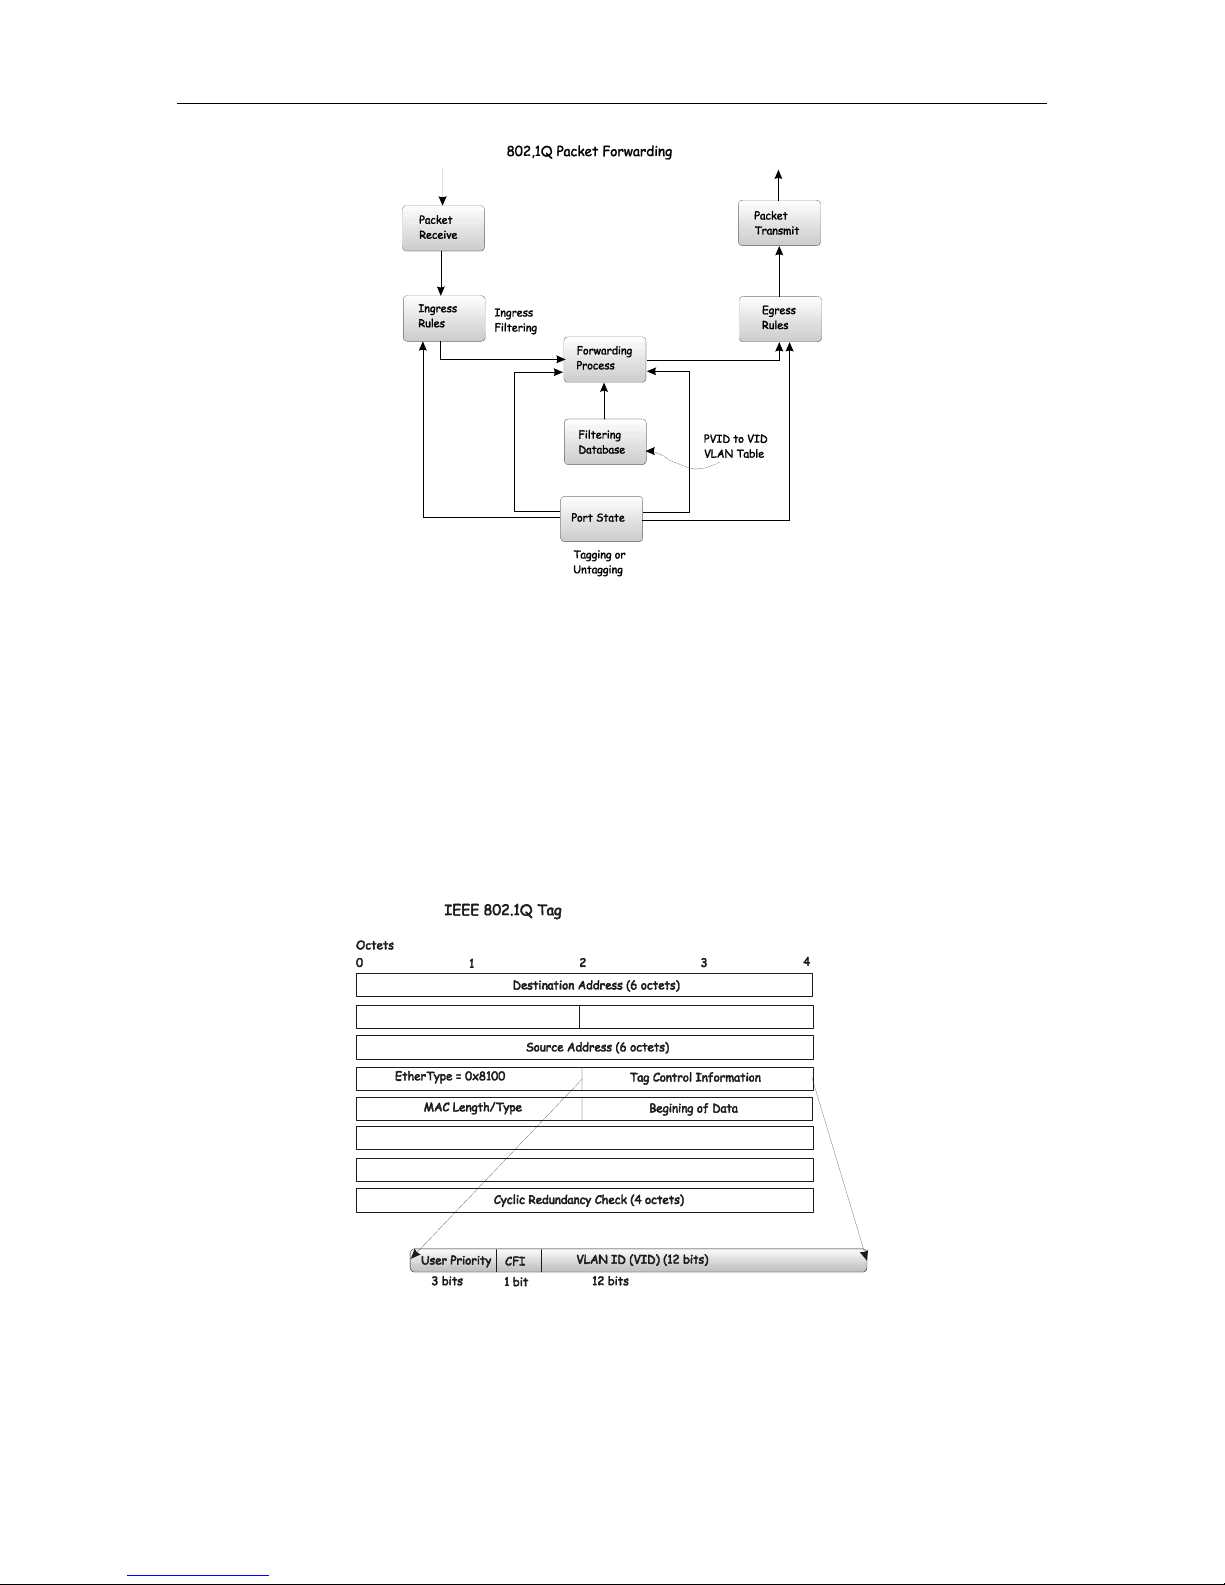
802.1Q VLAN Tags
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 17. 802.1Q Packet Forwarding
The figure below shows the 802.1Q VLAN tag. There are four additional octets inserted after the source
MAC address. Their presence is indicated by a value of 0x8100 in the EtherType field. When a packet’s
EtherType field is equal to 0x8100, the packet carries the IEEE 802.1Q/802.1p tag. The tag is contained in
the following two octets and consists of three bits or user priority, one bit of Canonical Format Identifier
(CFI – used for encapsulating Token Ring packets so they can be carried across Ethernet backbones) and
twelve bits of VLAN ID (VID). The three bits of user priority are used by 802.1p. The VID is the VLAN
identifier and is used by the 802.1Q standard. Because the VID is twelve bits long, 4094 unique VLANs
can be identified.
The tag is inserted into the packet header making the entire packet longer by four octets. All of the
information contained in the packet originally is retained.
The EtherType and VLAN ID are inserted after the MAC source address, but before the original
EtherType/Length or Logical Link Control. Because the packet is now a bit longer than it was originally,
the Cyclic Redundancy Check (CRC) must be recalculated.
Figure 4- 18. IEEE 802.1Q Tag
69
Page 70
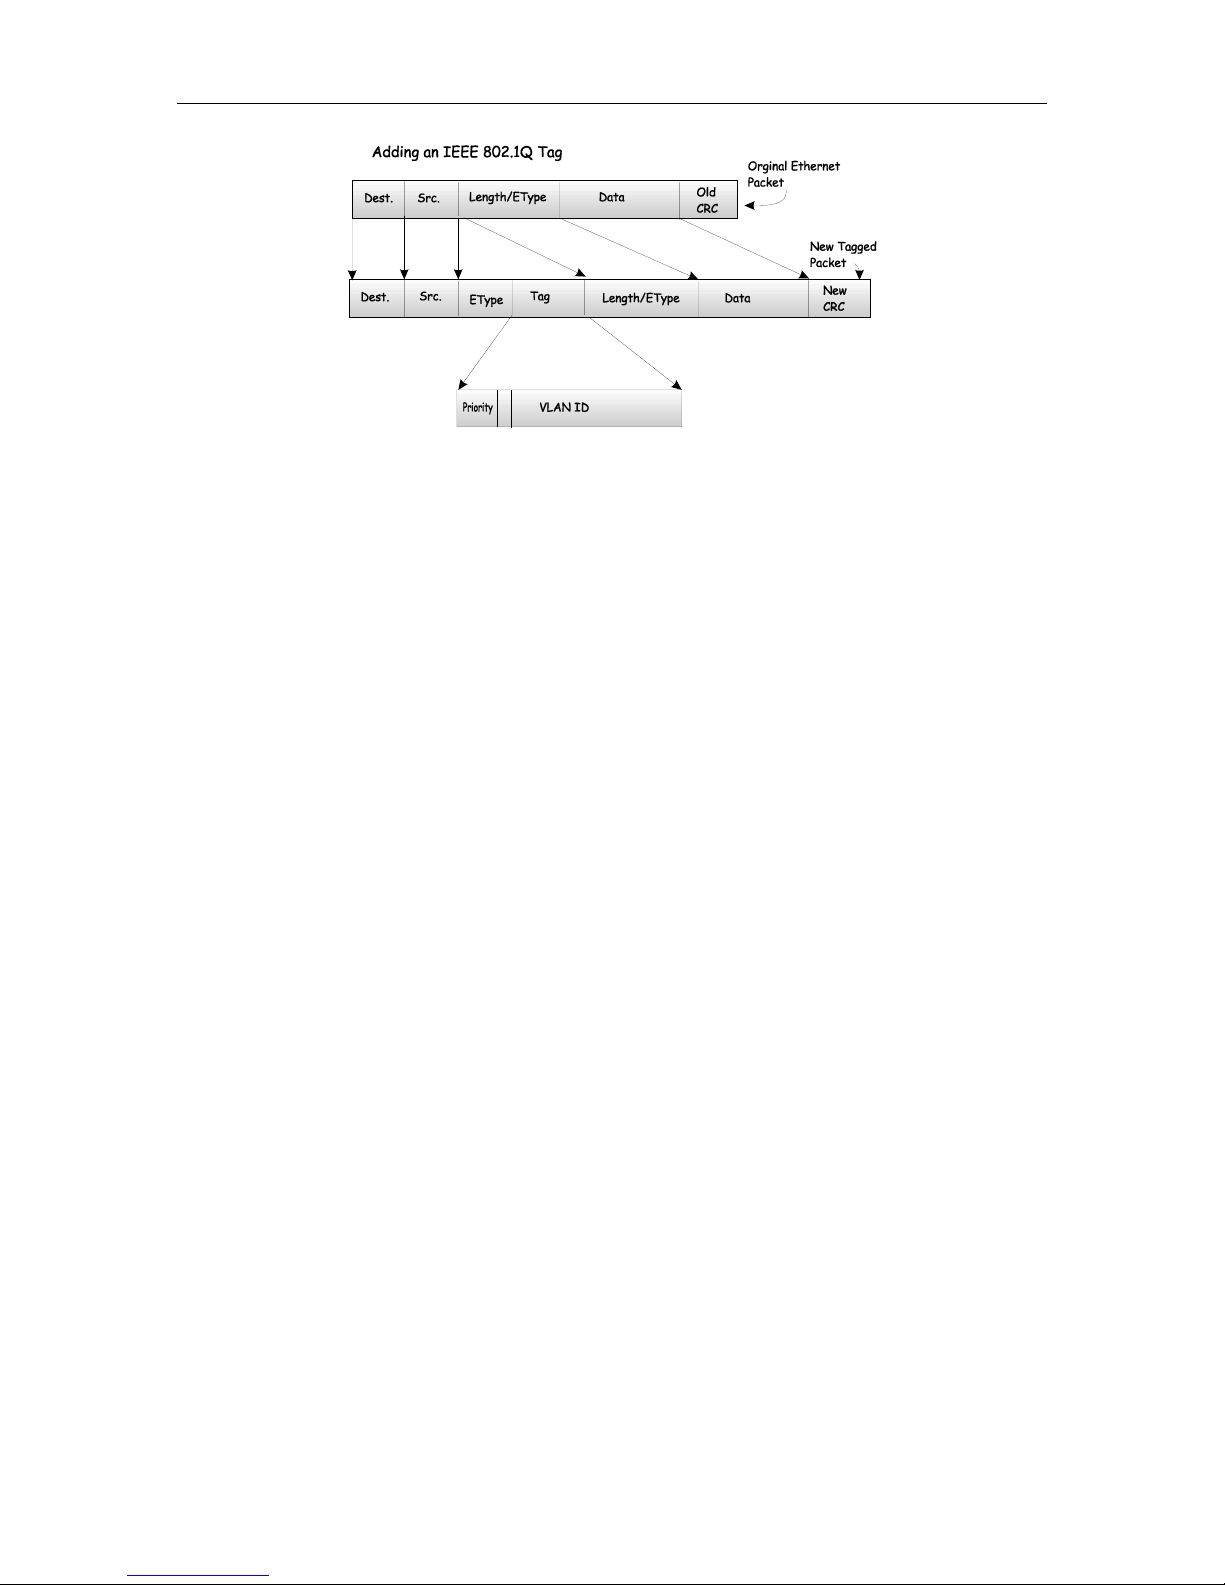
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 19. Adding an IEEE 802.1Q Tag
Port VLAN ID
Packets that are tagged (are carrying the 802.1Q VID information) can be transmitted from one 802.1Q
compliant network device to another with the VLAN information intact. This allows 802.1Q VLANs to
span network devices (and indeed, the entire network – if all network devices are 802.1Q compliant).
Unfortunately, not all network devices are 802.1Q compliant. These devices are referred to as tag-unaware.
802.1Q devices are referred to as tag-aware.
Prior to the adoption 802.1Q VLANs, port-based and MAC-based VLANs were in common use. These
VLANs relied upon a Port VLAN ID (PVID) to forward packets. A packet received on a given port would
be assigned that port’s PVID and then be forwarded to the port that corresponded to the packet’s
destination address (found in the Switch’s forwarding table). If the PVID of the port that received the
packet is different from the PVID of the port that is to transmit the packet, the Switch will drop the packet.
Within the Switch, different PVIDs mean different VLANs. (remember that two VLANs cannot
communicate without an external router). So, VLAN identification based upon the PVIDs cannot create
VLANs that extend outside a given Switch (or Switch stack).
Every physical port on a Switch has a PVID. 802.1Q ports are also assigned a PVID, for use within the
Switch. If no VLANs are defined on the Switch, all ports are then assigned to a default VLAN with a
PVID equal to 1. Untagged packets are assigned the PVID of the port on which they were received.
Forwarding decisions are based upon this PVID, in so far as VLANs are concerned. Tagged packets are
forwarded according to the VID contained within the tag. Tagged packets are also assigned a PVID, but the
PVID is not used to make packet forwarding decisions, the VID is.
Tag-aware Switches must keep a table to relate PVIDs within the Switch to VIDs on the network. The
Switch will compare the VID of a packet to be transmitted to the VID of the port that is to transmit the
packet. If the two VIDs are different, the Switch will drop the packet. Because of the existence of the PVID
for untagged packets and the VID for tagged packets, tag-aware and tag-unaware network devices can
coexist on the same network.
A Switch port can have only one PVID, but can have as many VIDs as the Switch has memory in its
VLAN table to store them.
Because some devices on a network may be tag-unaware, a decision must be made at each port on a tagaware device before packets are transmitted – should the packet to be transmitted have a tag or not? If the
transmitting port is connected to a tag-unaware device, the packet should be untagged. If the transmitting
port is connected to a tag-aware device, the packet should be tagged.
Tagging and Untagging
Every port on an 802.1Q compliant Switch can be configured as tagging or untagging.
Ports with tagging enabled will put the VID number, priority and other VLAN information into the header
of all packets that flow into and out of it. If a packet has previously been tagged, the port will not alter the
packet, thus keeping the VLAN information intact. The VLAN information in the tag can then be used by
other 802.1Q compliant devices on the network to make packet forwarding decisions.
70
Page 71
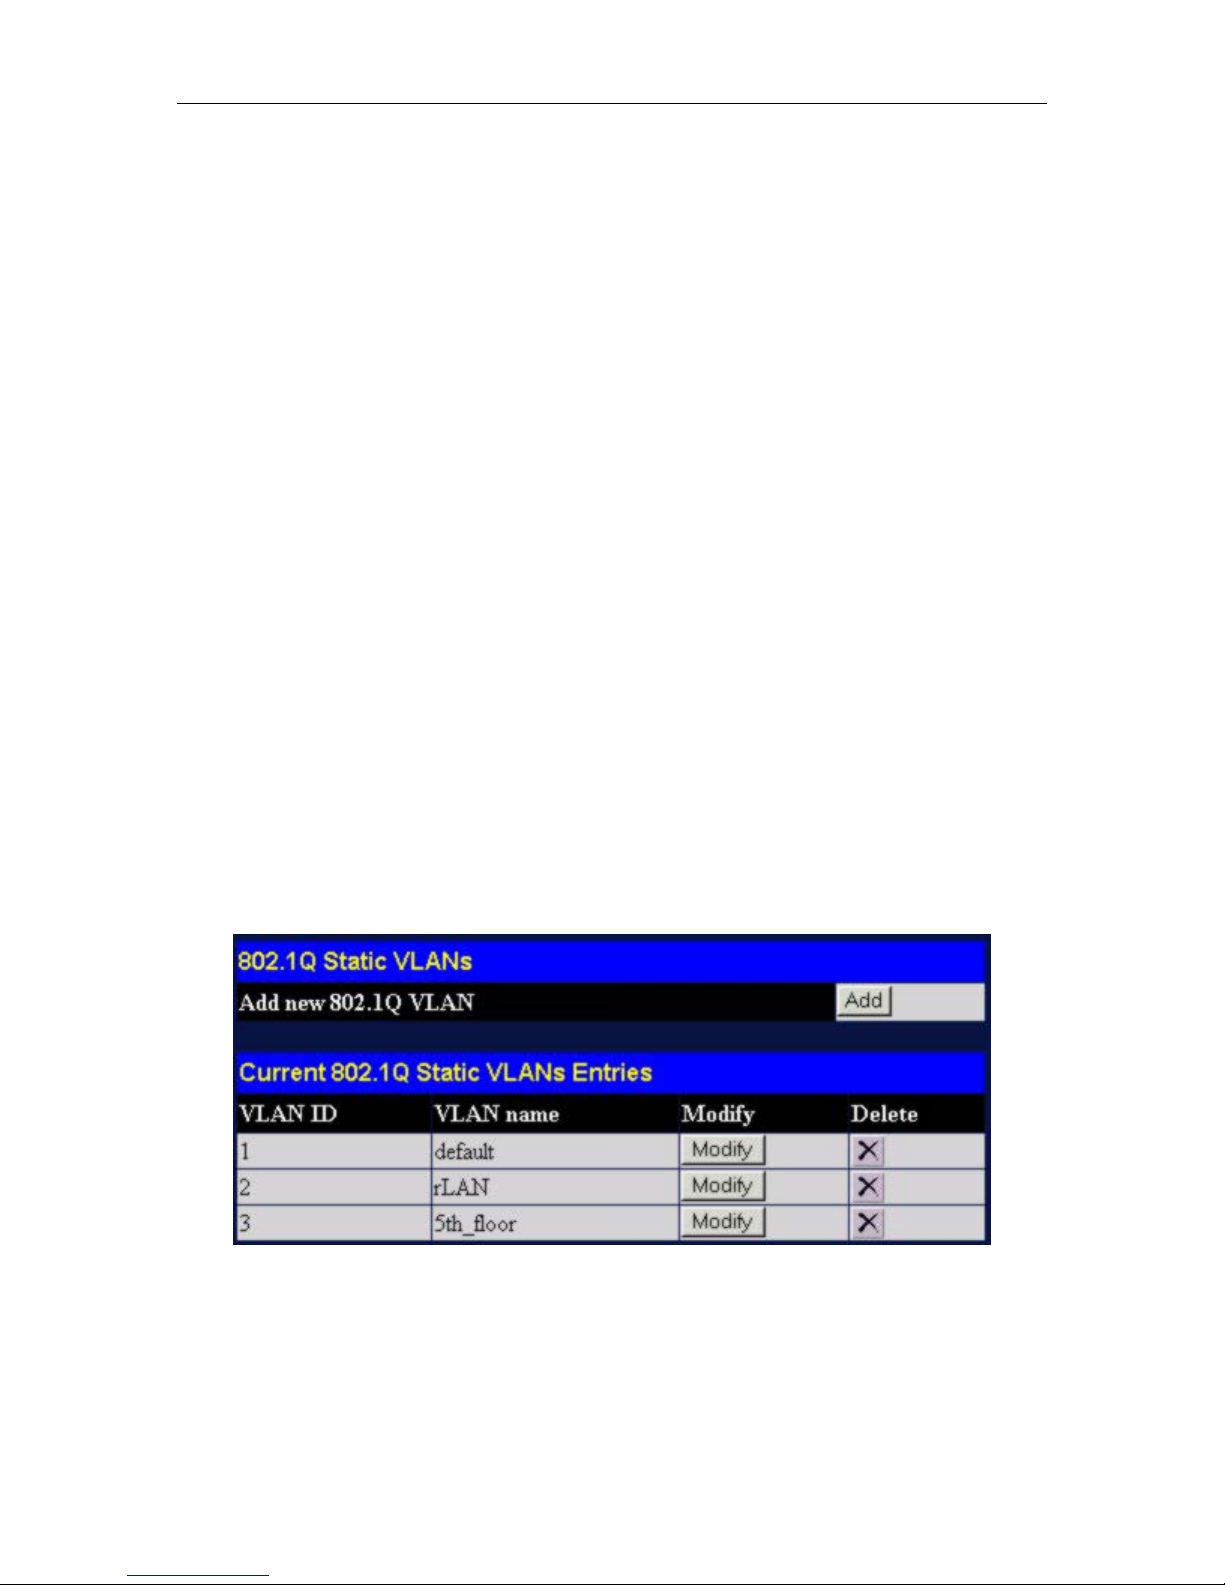
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Ports with untagging enabled will strip the 802.1Q tag from all packets that flow into and out of those ports.
If the packet doesn’t have an 802.1Q VLAN tag, the port will not alter the packet. Thus, all packets
received by and forwarded by an untagging port will have no 802.1Q VLAN information. (Remember that
the PVID is only used internally within the Switch). Untagging is used to send packets from an 802.1Qcompliant network device to a non-compliant network device.
Ingress Filtering
A port on a Switch where packets are flowing into the Switch and VLAN decisions must be made is
referred to as an ingress port. If ingress filtering is enabled for a port, the Switch will examine the VLAN
information in the packet header (if present) and decide whether or not to forward the packet.
If the packet is tagged with VLAN information, the ingress port will first determine if the ingress port itself
is a member of the tagged VLAN. If it is not, the packet will be dropped. If the ingress port is a member of
the 802.1Q VLAN, the Switch then determines if the destination port is a member of the 802.1Q VLAN. If
it is not, the packet is dropped. If the destination port is a member of the 802.1Q VLAN, the packet is
forwarded and the destination port transmits it to its attached network segment.
If the packet is not tagged with VLAN information, the ingress port will tag the packet with its own PVID
as a VID (if the port is a tagging port). The Switch then determines if the destination port is a member of
the same VLAN (has the same VID) as the ingress port. If it does not, the packet is dropped. If it has the
same VID, the packet is forwarded and the destination port transmits it on its attached network segment.
This process is referred to as ingress filtering and is used to conserve bandwidth within the Switch by
dropping packets that are not on the same VLAN as the ingress port at the point of reception. This
eliminates the subsequent processing of packets that will just be dropped by the destination port.
802.1Q Static VLANs
To create or modify an 802.1Q VLAN:
In the Configuration folder, open the VLANs folder and click the Static VLAN Entry link to open the
following window:
Figure 4- 20. 802.1Q Static VLANs Entries table
The first 802.1Q Static VLANs window lists all previously configured VLANs by VLAN ID and name.
To delete an existing 802.1Q VLAN, click the corresponding Delete button.
To create a new 802.1Q VLAN, click the Add button. A new window appears, use this to configure the
port settings and to assign a unique name and number to the new VLAN. See the table below for a
description of the parameters in the new window.
71
Page 72
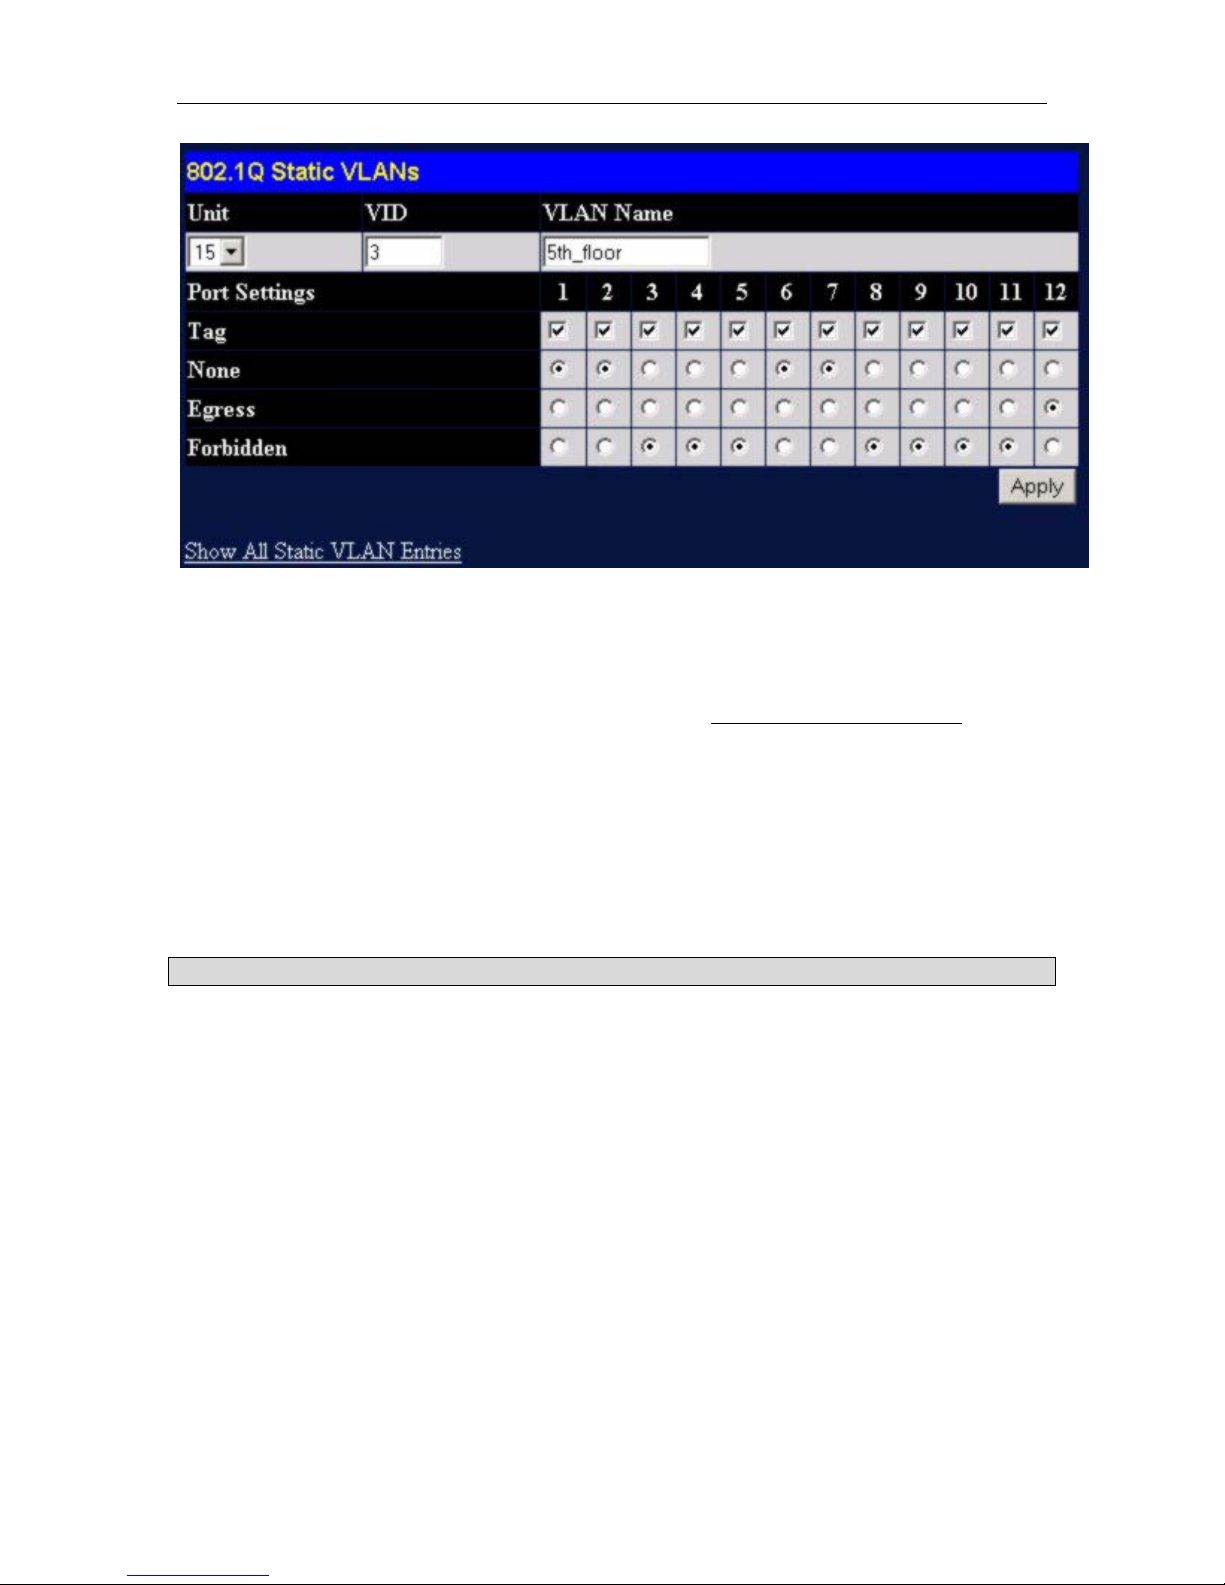
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 21. 802.1Q Static VLANs menu
To configure the newly created VLAN, select the Switch being configured from the Unit drop-down menu
and provide a unique VLAN identifier and name. Configure the port settings for VLAN membership by
selecting the appropriate options for each port. Click the Apply button to configure the VLAN port
membership settings. A success or fail message appears to confirm whether the settings have been applied.
To view the VLANs that have been thus far configured, click the Show All Static VLAN Entries
hyperlink
(see example below). To add another new VLAN entry, click the Add button again in the first 802.1Q
Static VLANs window.
See the table below for a description of the port VLAN membership settings.
The following fields can then be set in either the Add or Modify 802.1Q Static VLANs windows:
Parameter Description
Unit
Choose the Switch that the VLAN will be created on.
VID (VLAN ID) For a new VLAN entry, type in a unique identifier. This number is used to
configure other settings such as GVRP status for ports in the VLAN.
VLAN Name
For a new VLAN entry type in a unique name. This name can be used to
identify the VLAN for IP interface assignment. Remember that VLAN
names are case-sensitive when referring to them for other applications
(such as setting up IP interfaces).
Port
Configure each individual port to be specified as member or nonmember
of the VLAN.
Tag
None
Specifies the port as either 802.1Q tagging or 802.1Q untagged.
Checking the box will designate the port as Tagged.
Specifies the port as not being a static member of the VLAN, but with no
72
Page 73

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
restrictions for joining the VLAN dynamically through GVRP.
Egress
Select this to specify the port as a static member of the VLAN. Egress
member ports are ports that will be transmitting traffic for the VLAN.
These ports can be either tagged or untagged.
Forbidden
Select this to specify the port as not being a member of the VLAN and
that the port is forbidden from becoming a member of the VLAN
dynamically.
The illustration below displays the port settings for a new VLAN (engineering) with a VID of 11.
Figure 4- 22. Add New Static VLAN Example menu
Click the Show All Static VLAN
Entries link to return to the first 802.1Q Static VLANs window, the new
VLAN entry appears listed in the current entries table.
Figure 4- 23. 802.1Q Static VLANs With Added VLAN menu
To change the port settings of any listed VLAN, click the Modify button.
Now click the Modify button in the first 802.1Q Static VLANs window for the newly created VLAN
(engineering). A new window appears, use this to configure the port settings to the existing VLAN, exactly
73
Page 74

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
as in the add new VLAN window. Notice that the VID and name cannot be changed. If you want to change
the VID or VLAN Name it will be necessary to delete the existing entry and create a new one.
Figure 4- 24. 802.1Q Static VLANs – Modify menu
GVRP Setting
Open the 802.1Q Port Settings window and select the Unit and range of ports to configure. For the
selected port or group of ports, choose to enable or disable Ingress checking and establish an acceptable
packet rule. Ingress Checking is used to limit traffic by filtering incoming packets that have a PVID does
not match the PVID of the port. 802.1Q port settings are also used to determine whether the Switch will
share its VLAN configuration information with GARP VLAN Registration Protocol (GVRP) enabled
Switches.
The window and table below describe how to configure the 802.1Q VLAN port settings for the Switch.
74
Page 75

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 25. 802.1Q Port Settings and entries table
Configure the 802.1 Port Settings:
Parameter Description
Unit
From [ ] To [ ]
Select the relevant Switch for configuration.
Use these drop-down menus to specify the range of ports that will be
included in the VLAN.
This field can be toggled using the space bar between Enabled and
Disabled. Enabled enables the port to compare the VID tag of an
Ingress Check
incoming packet with the PVID number assigned to the port. If the two are
different, the port filters (drops) the packet. Disabled disables Ingress
filtering. Ingress Checking is disabled by default.
Allows you to specify the action the Switch will take when a packet is
received. If you specify Admit_all the Switch will receive and forward all
Frame Type
packets to this VLAN regardless of whether or not the packet has an
802.1Q VLAN tag or not. If you specify Tagged_only the Switch will drop
and untagged packets it receives for this VLAN.
A Port VLAN Identifier is a classification mechanism that associates a port
with a specific VLAN and is used to make forwarding decisions for
PVID
untagged packets received by the port. For example, if port 2 is assigned
a PVID of 3, then all untagged packets received on port 2 will be assigned
to VLAN 3. This number is generally the same as the VID number
assigned to the port in the Edit 802.1Q VLANs window above.
75
Page 76
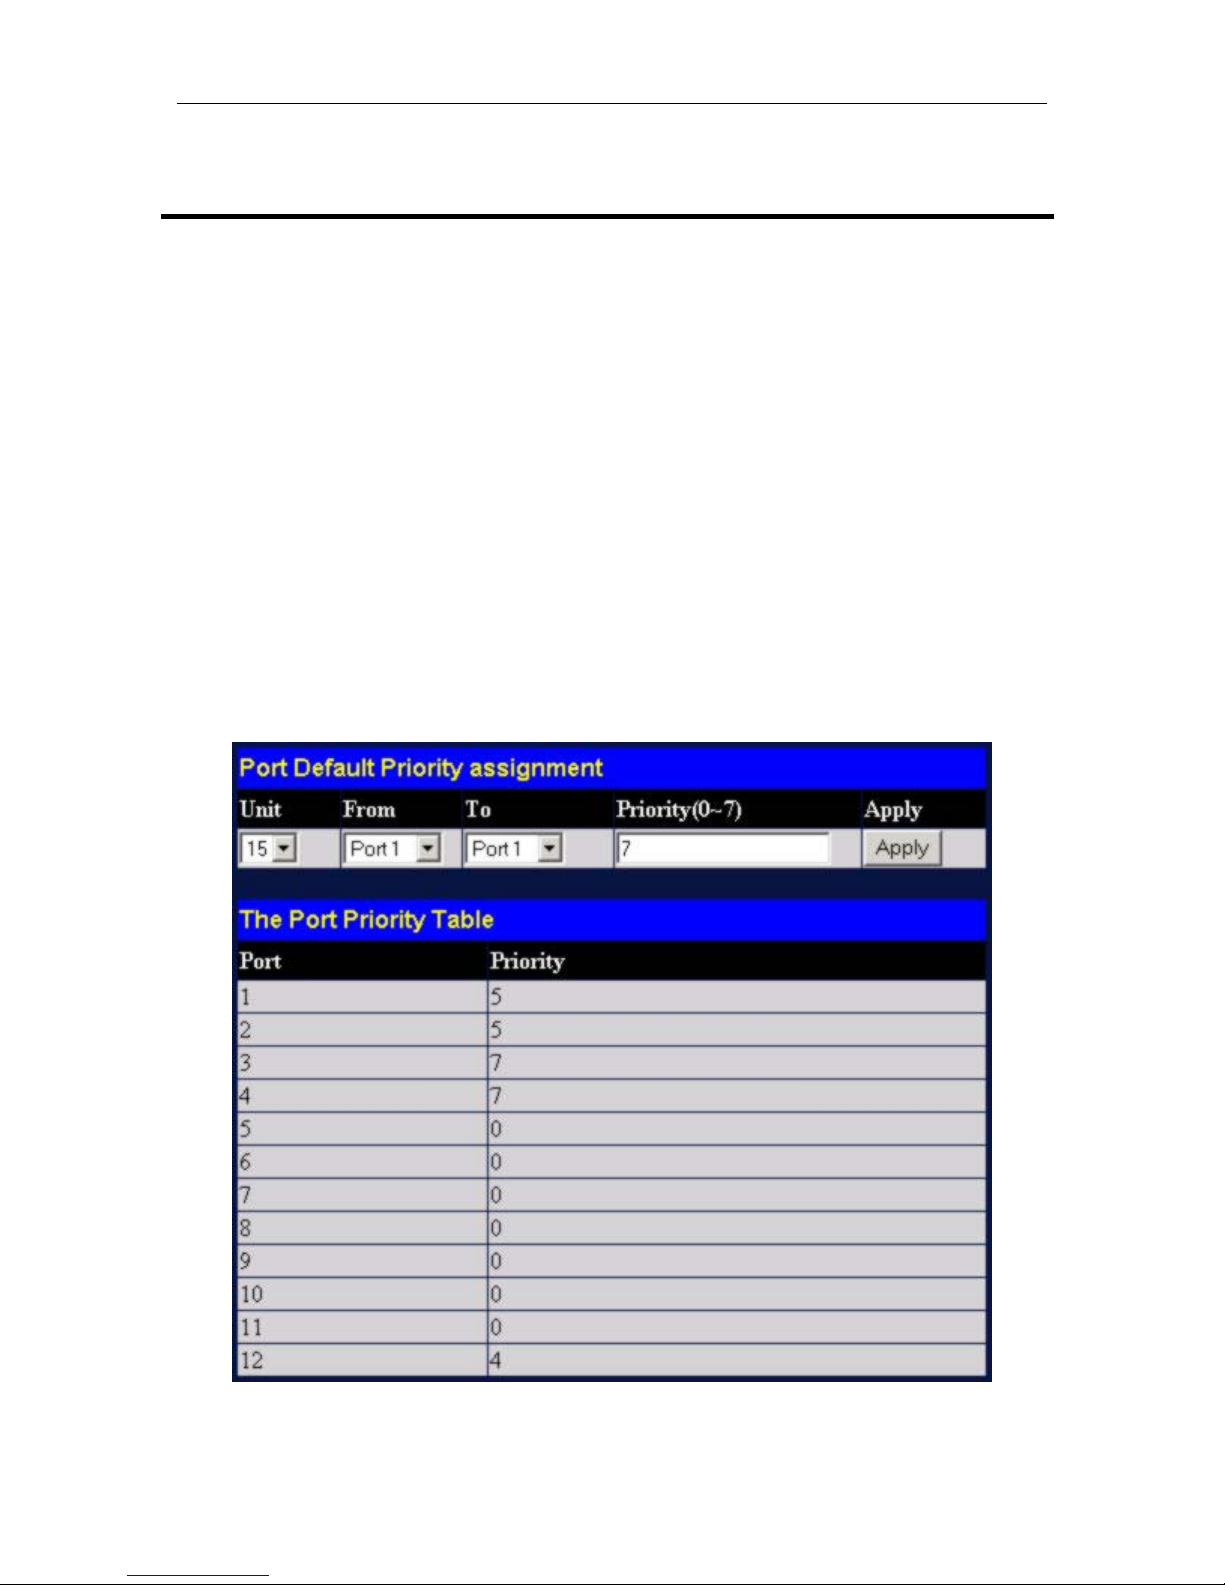
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
GVRP
The Group VLAN Registration Protocol (GVRP) enables the port to
dynamically become a member of a VLAN. GVRP is disabled by default.
QoS
QoS settings allow customization of packet priority in order to facilitate delivery of data traffic that might
be affected by latency problems. The IEEE 802.1p Priority specification uses eight priority levels to
classify data packets. In 802.1p compliant devices, a tag inserted into the packet header is used to identify
the priority level of data packets.
The Switch implements 802.1p priority using four hardware queues instead of eight. Therefore the Switch
must have a means of mapping the eight levels specified in the IEEE 802.1p standard to the four hardware
queues used in the Switch. This is done using the Class of Service menu explained below. Further
customization of priority classification can be done with the Output Scheduling menu, also explained below.
Individual ports may still be assigned priority using the eight levels as defined by the 802.1p standard.
It is important to note that changes in a networks QoS scheme should be carefully considered, planned for
and if possible tested for efficiency. When set up properly, it QoS can allow efficient and timely delivery of
data for video conferencing or IP telephony without causing unacceptable delays of other network traffic. If
QoS is not well set up however, significant delays and excessive packet loss may result for data assigned to
lower priority queues.
802.1p Default Priority
The Switch allows the assignment of a default 802.1p priority to each port on the Switch.
Click on the 802.1p Default Priority link in the QoS sub-folder:
Figure 4- 26. Port Default Priority assignment menu
76
Page 77
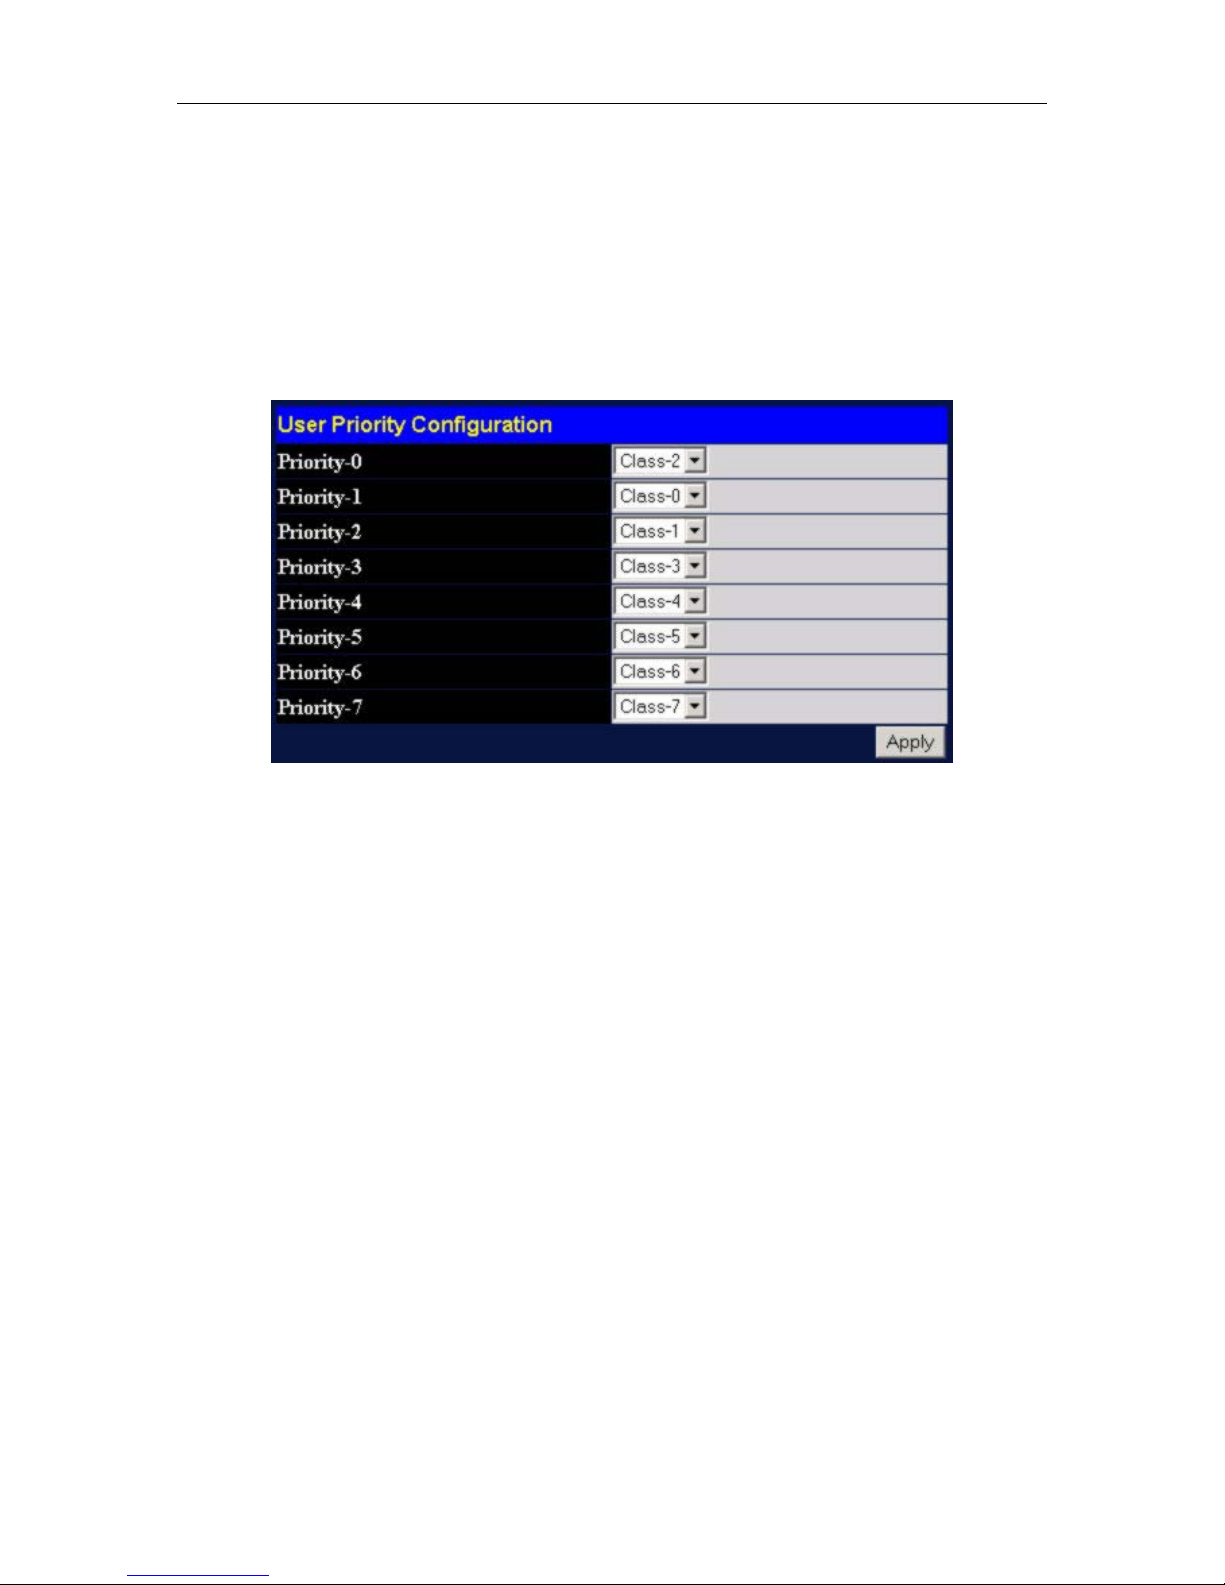
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
This page allows you to assign a default 802.1p priority to any given port on the Switch. The priority
queues are numbered from 0 − the lowest priority − to 7 − the highest priority.
802.1p User Priority
The GSW-1290 allows the assignment of a User Priority to each of the 802.1p priorities.
Figure 4- 27. User Priority Configuration menu
Once you have assigned a priority to the port groups on the Switch, you can then assign this Class to each
of the eight levels of 802.1p priorities.
QoS Output Scheduling Configuration
QoS can be customized by changing the output scheduling used for the hardware queues in the Switch. As
with any changes to QoS implementation, careful consideration should be given to how network traffic in
lower priority queues are affected. Changes in scheduling may result in unacceptable levels of packet loss
or significant transmission delay. If you choose to customize this setting, it is important to monitor network
performance, especially during peak demand as bottlenecks can quickly develop if the QoS settings are not
suitable.
77
Page 78
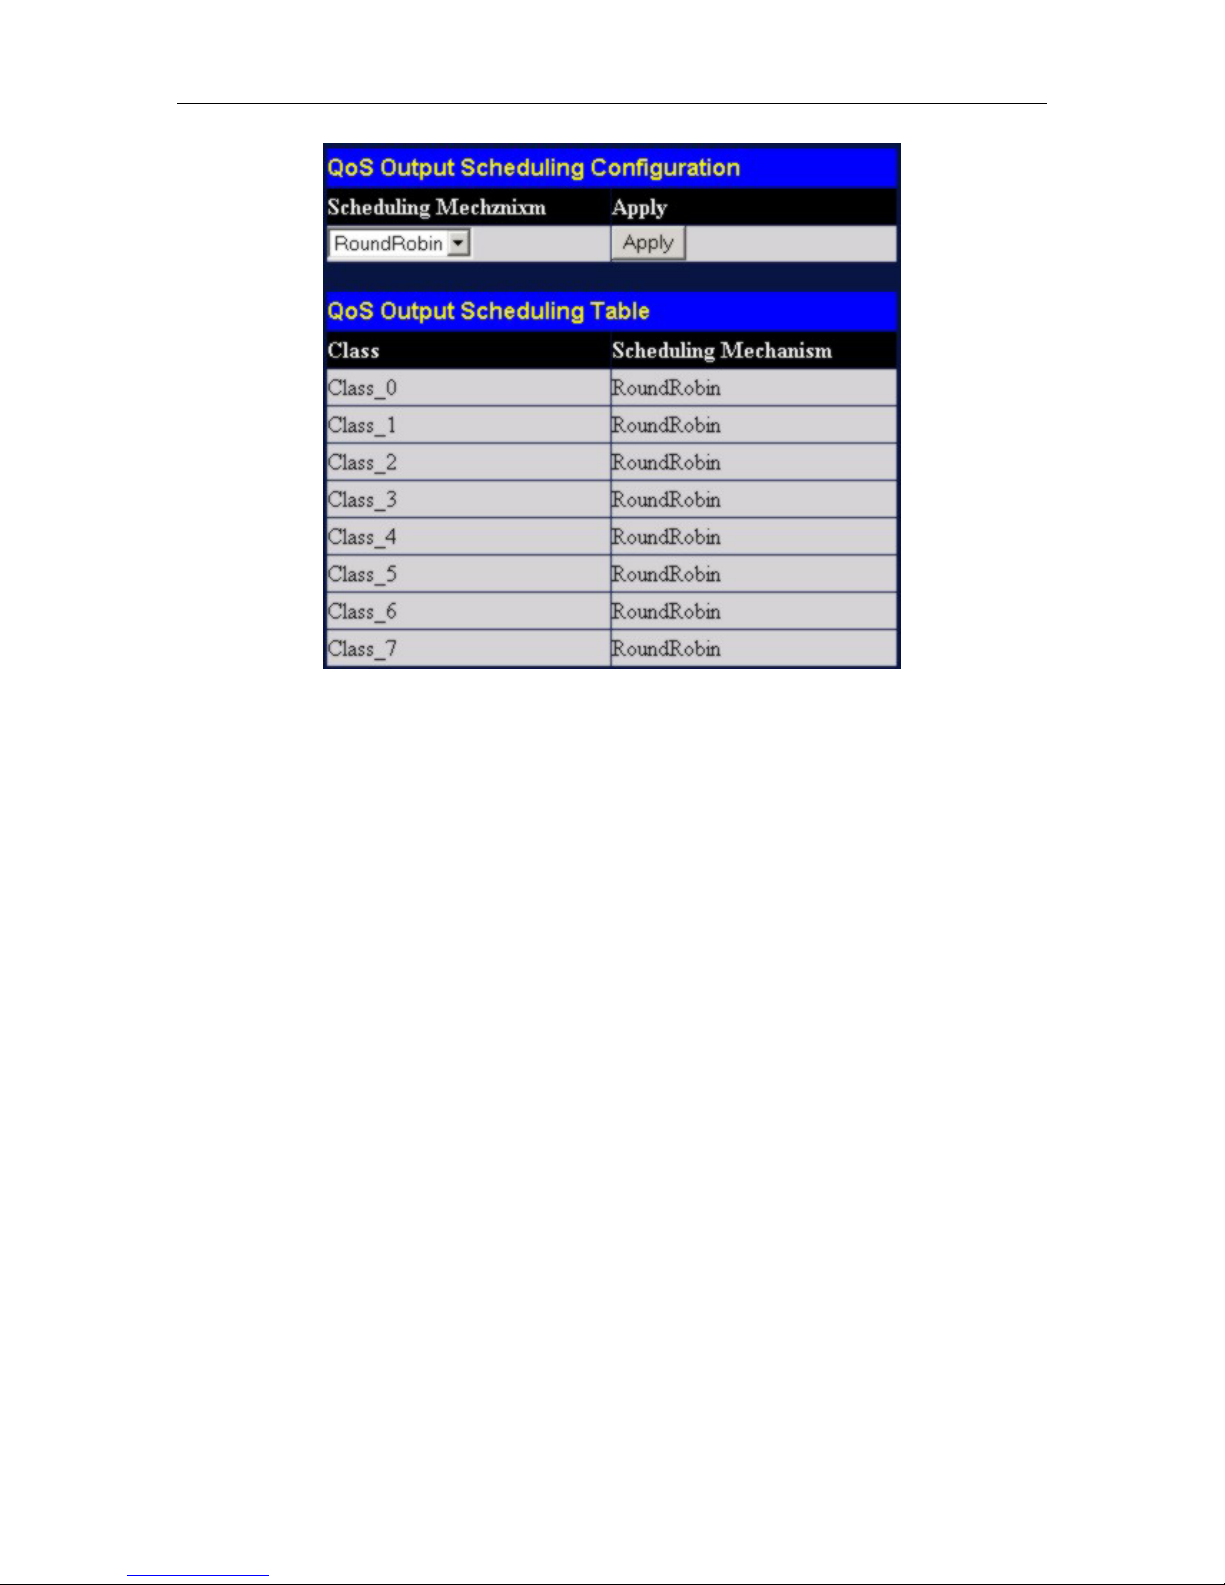
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 28. QoS Output Scheduling Configuration menu
Use the Scheduling Mechanism drop-down menu to select between a RoundRobin and a Strict mechanism
for empting the priority queues.
Click Apply to let your changes take effect.
Traffic Segmentation
Traffic segmentation is used to limit traffic flow from a single port to a group of ports on either a single
Switch (in standalone mode) or a group of ports on another Switch in a Switch stack. This method of
segmenting the flow of traffic is similar to using VLANs to limit traffic, but is more restrictive. It provides
a method of directing traffic that does not increase the overhead of the Master Switch CPU.
78
Page 79
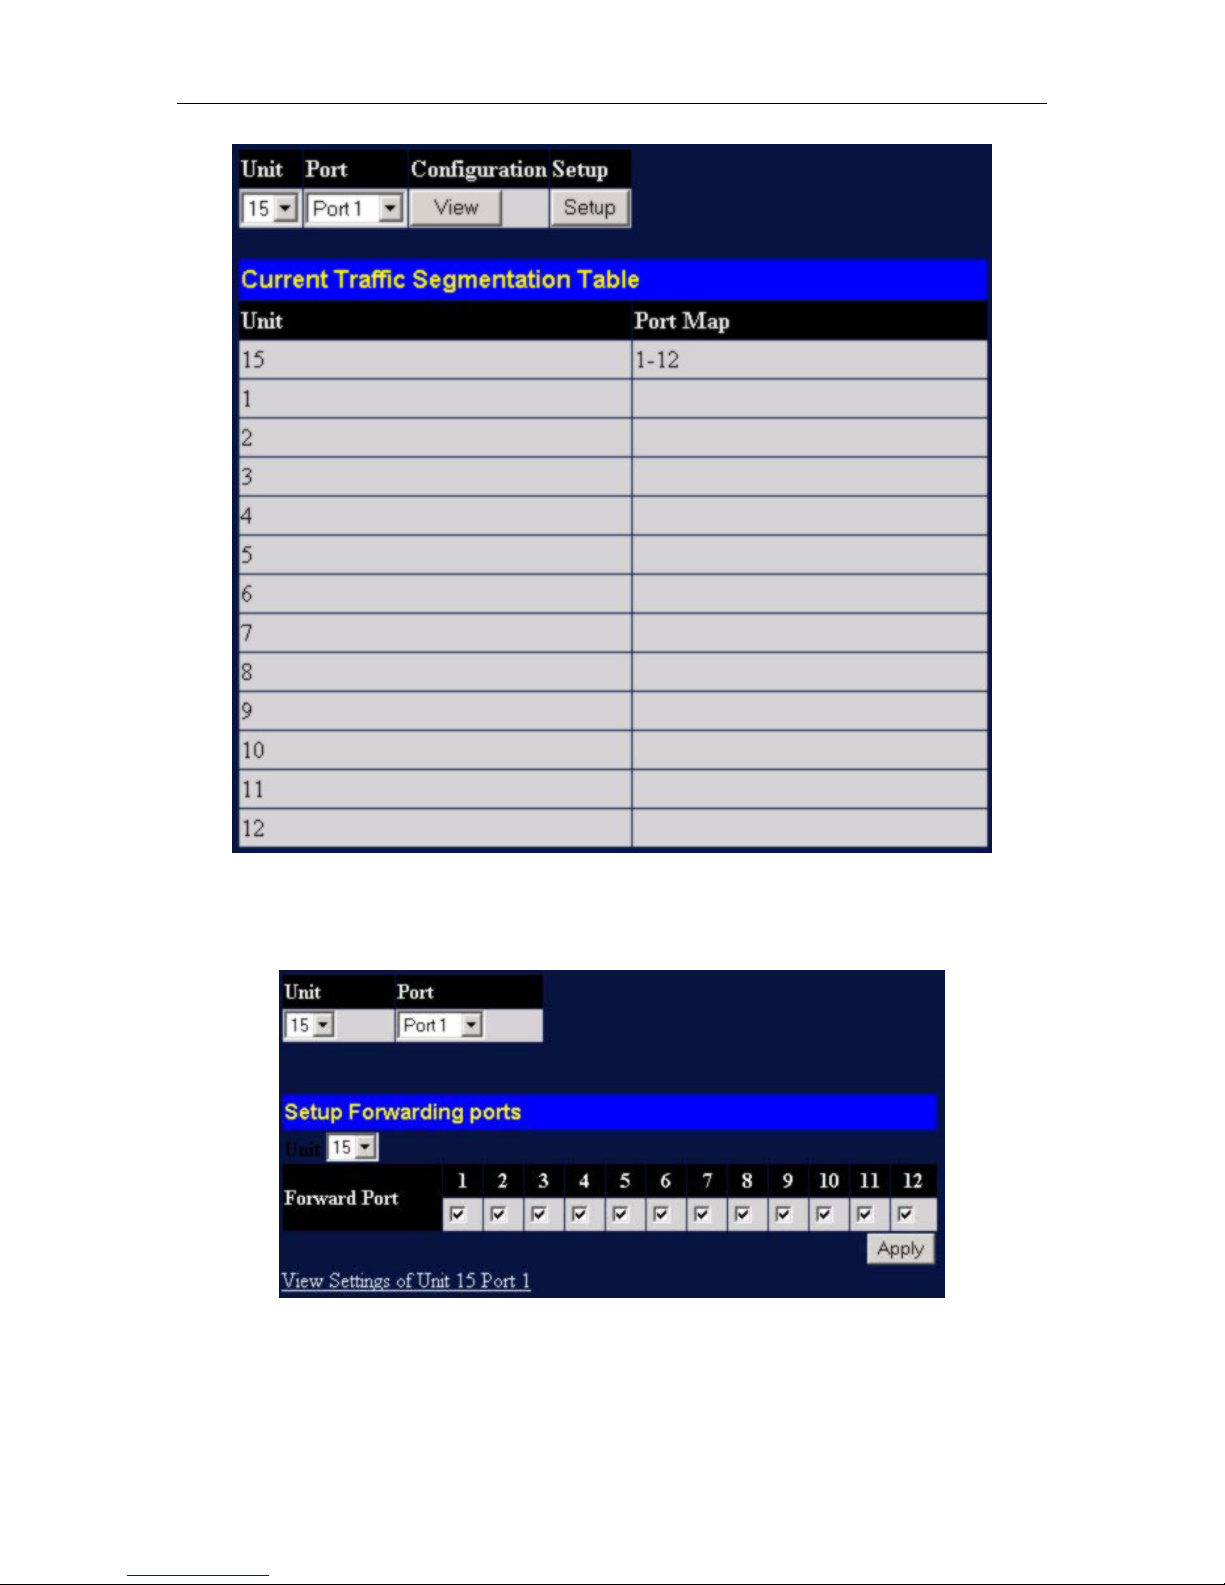
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 29. Traffic Segmentation table
The Unit drop-down menu at the top of the page allows you to select a Switch from a Switch stack using
that Switch’s Unit ID. The Port drop-down menu allows you to select a port from that Switch. This is the
port that will be transmitting packets.
Figure 4- 30. Traffic Segmentation Setup menu
79
Page 80
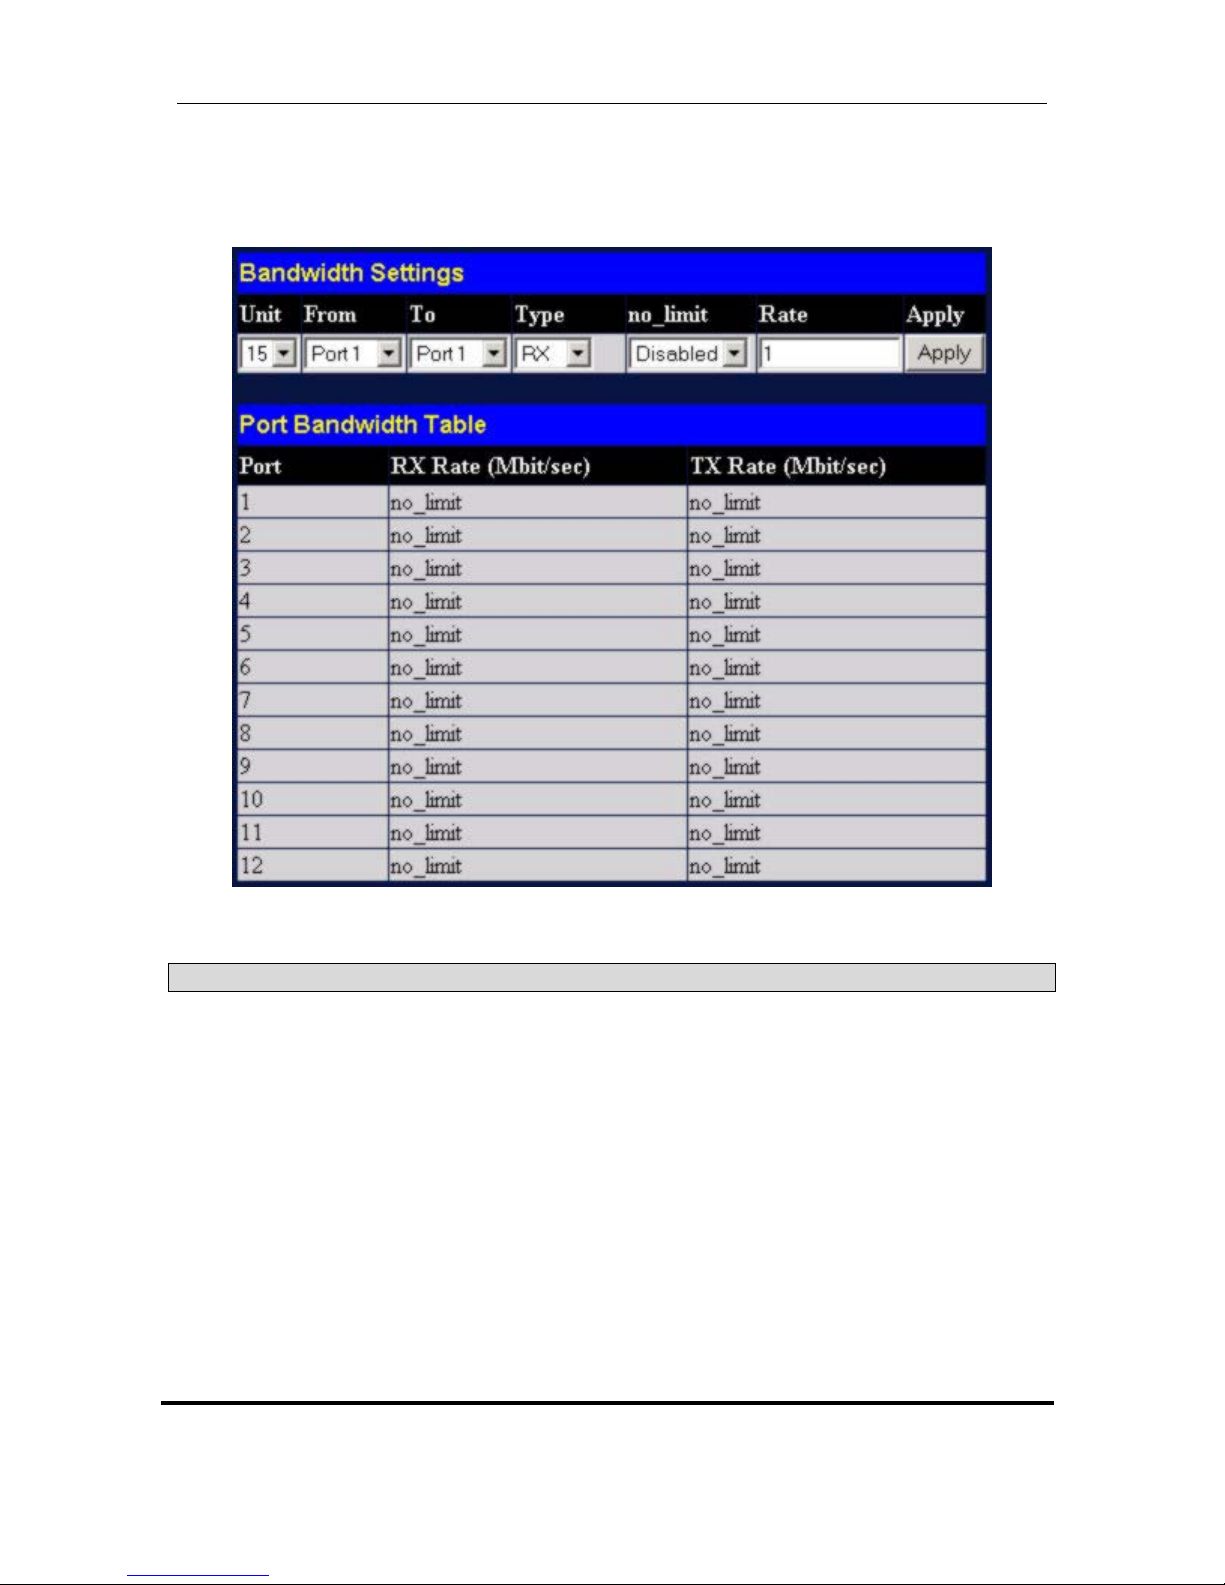
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Bandwidth Control
The bandwidth control settings are used to place a ceiling on the transmitting and receiving data rates for
any selected port.
Figure 4- 31. Bandwidth Settings menu
The following parameters can be set or are displayed:
Parameter Description
Unit
Allows you to specify a Switch in a Switch stack using that Switch’s Unit
ID. The number 15 indicates a Switch in standalone mode.
From/To
A consecutive group of ports may be configured starting with the selected
port.
Type
This drop-down menu allows you to select between RX (receive,) TX
(transmit,) and Both. This setting will determine whether the bandwidth
ceiling is applied to receiving, transmitting, or both receiving and
transmitting packets.
no_limit
This drop-down menu allows you to specify that the selected port will
have no bandwidth limit. Enabled disables the limit.
Rate
This field allows you to enter the data rate, in kb/s, that will be the limit for
the selected port.
80
Page 81
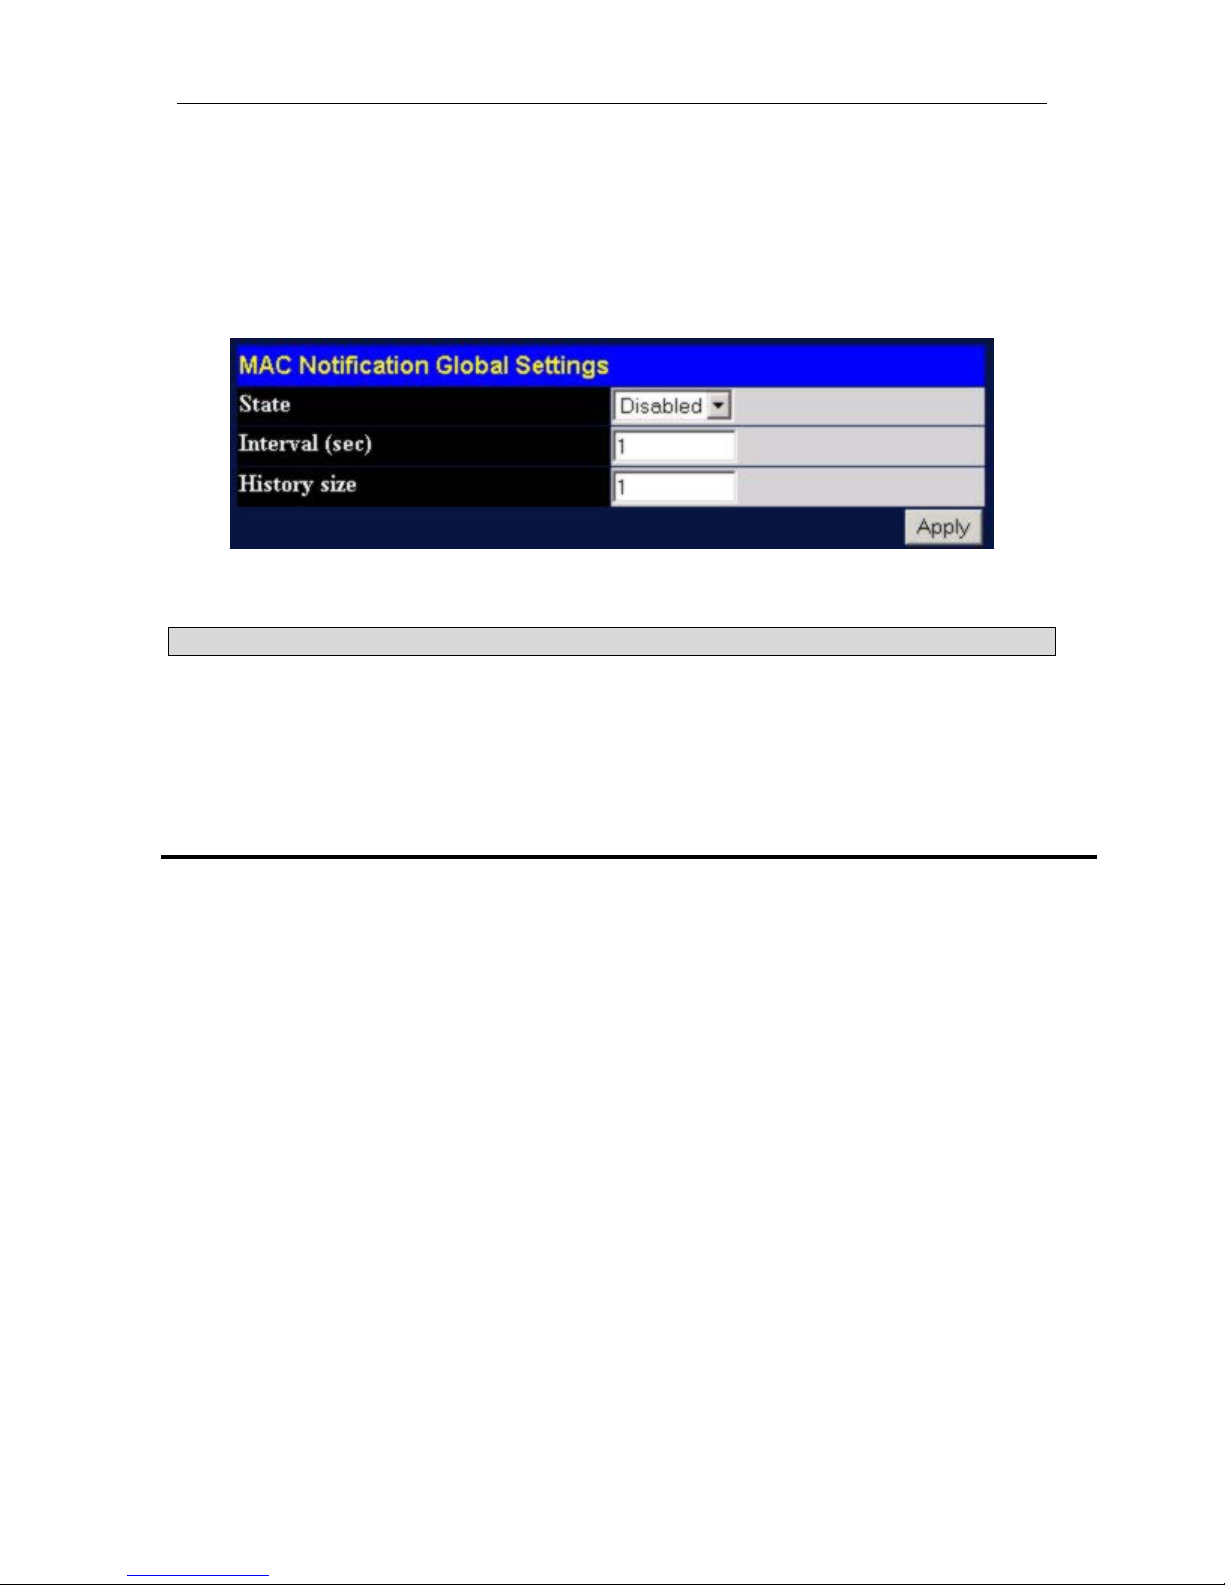
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
MAC Notification
MAC address notification is used to monitor MAC addresses as they are learned and entered into the
Switch’s MAC forwarding database.
Global Settings
Figure 4- 32. MAC Notification Global Settings menu
The following parameters can be set:
Parameter Description
State
Interval (sec)
History size
This drop-down menu is used to enable or disable MAC notification on the
selected Switch.
The time in seconds between notifications.
The maximum number of entries that will be listed in the History log. Up to 500
entries can be specified.
81
Page 82
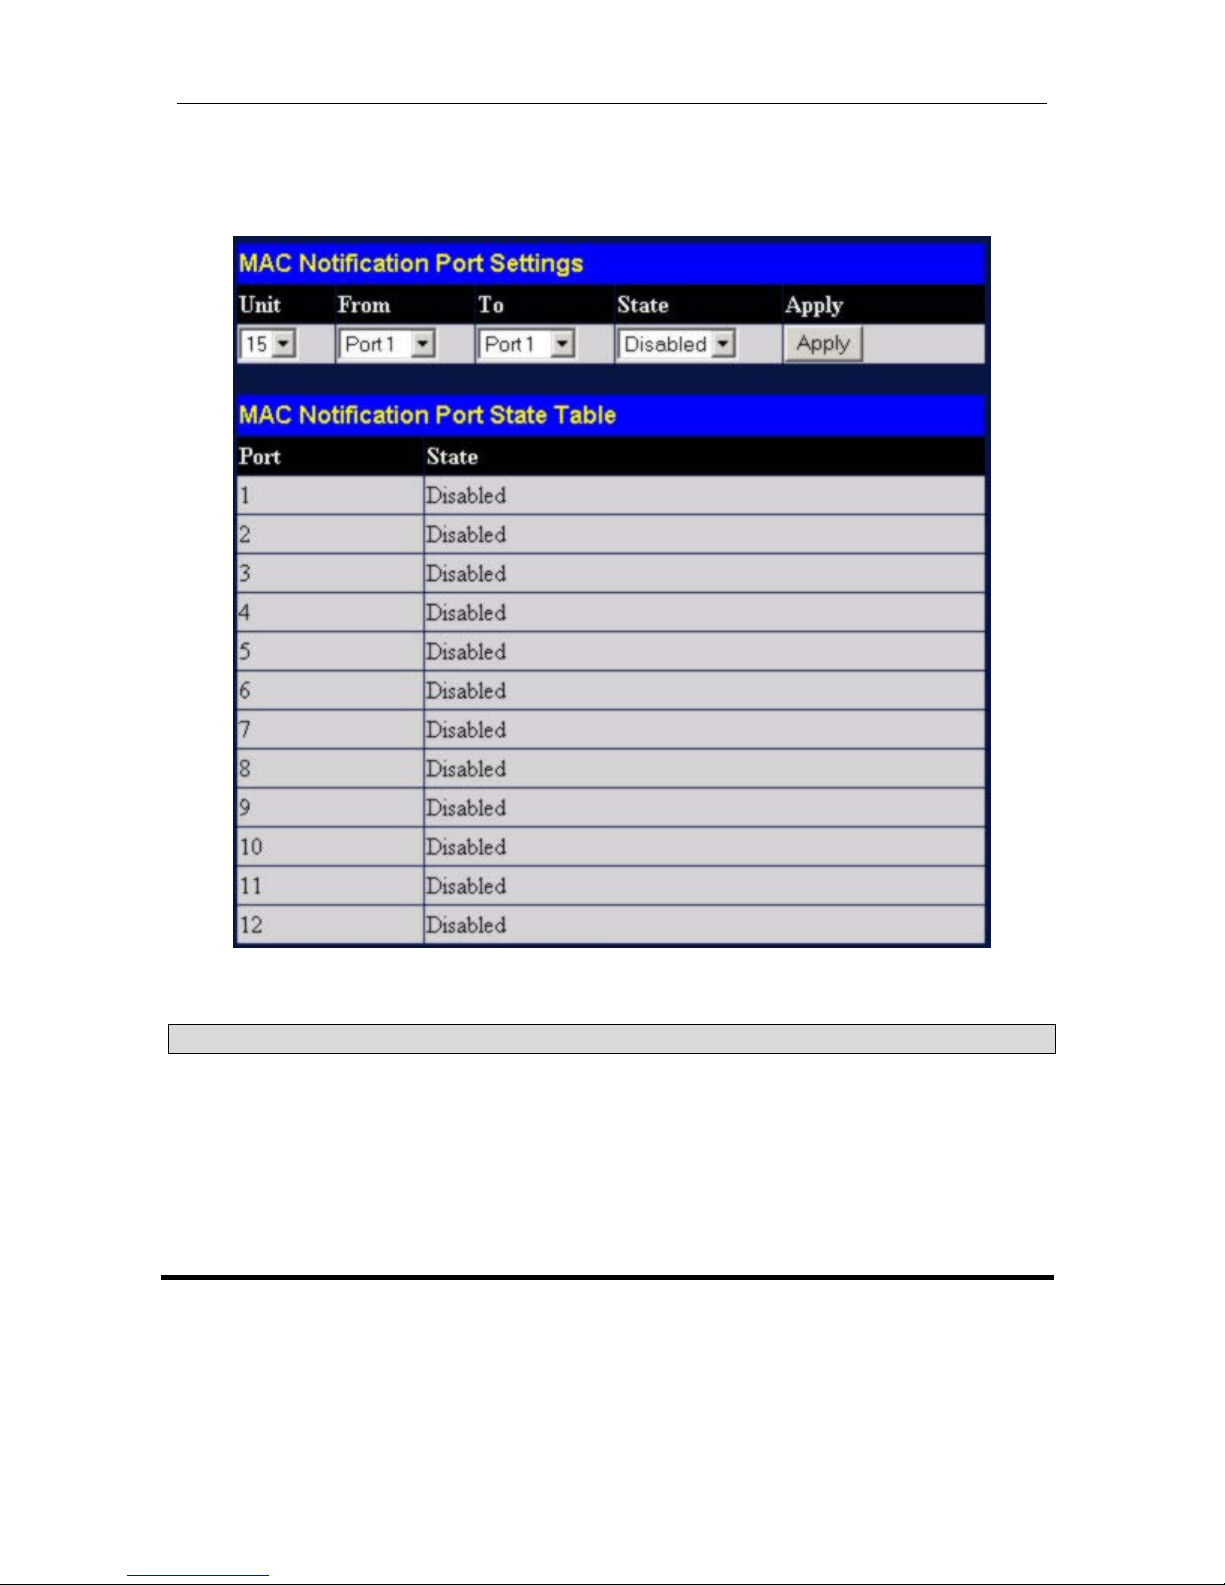
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Port Settings
Enable or disable MAC notification for ports with the window below.
Figure 4- 33. MAC Notification Port Settings menu
The following parameters can be set:
Parameter Description
Unit
Allows you to specify a Switch in a Switch stack using that Switch’s Unit
ID. Number 15 indicates a Switch in standalone mode.
From/To
A consecutive group of ports may be configured starting with the selected
port.
State
This pull-down menu allows you to enable or disable MAC notification for
the specified Switch and group of ports.
82
Page 83
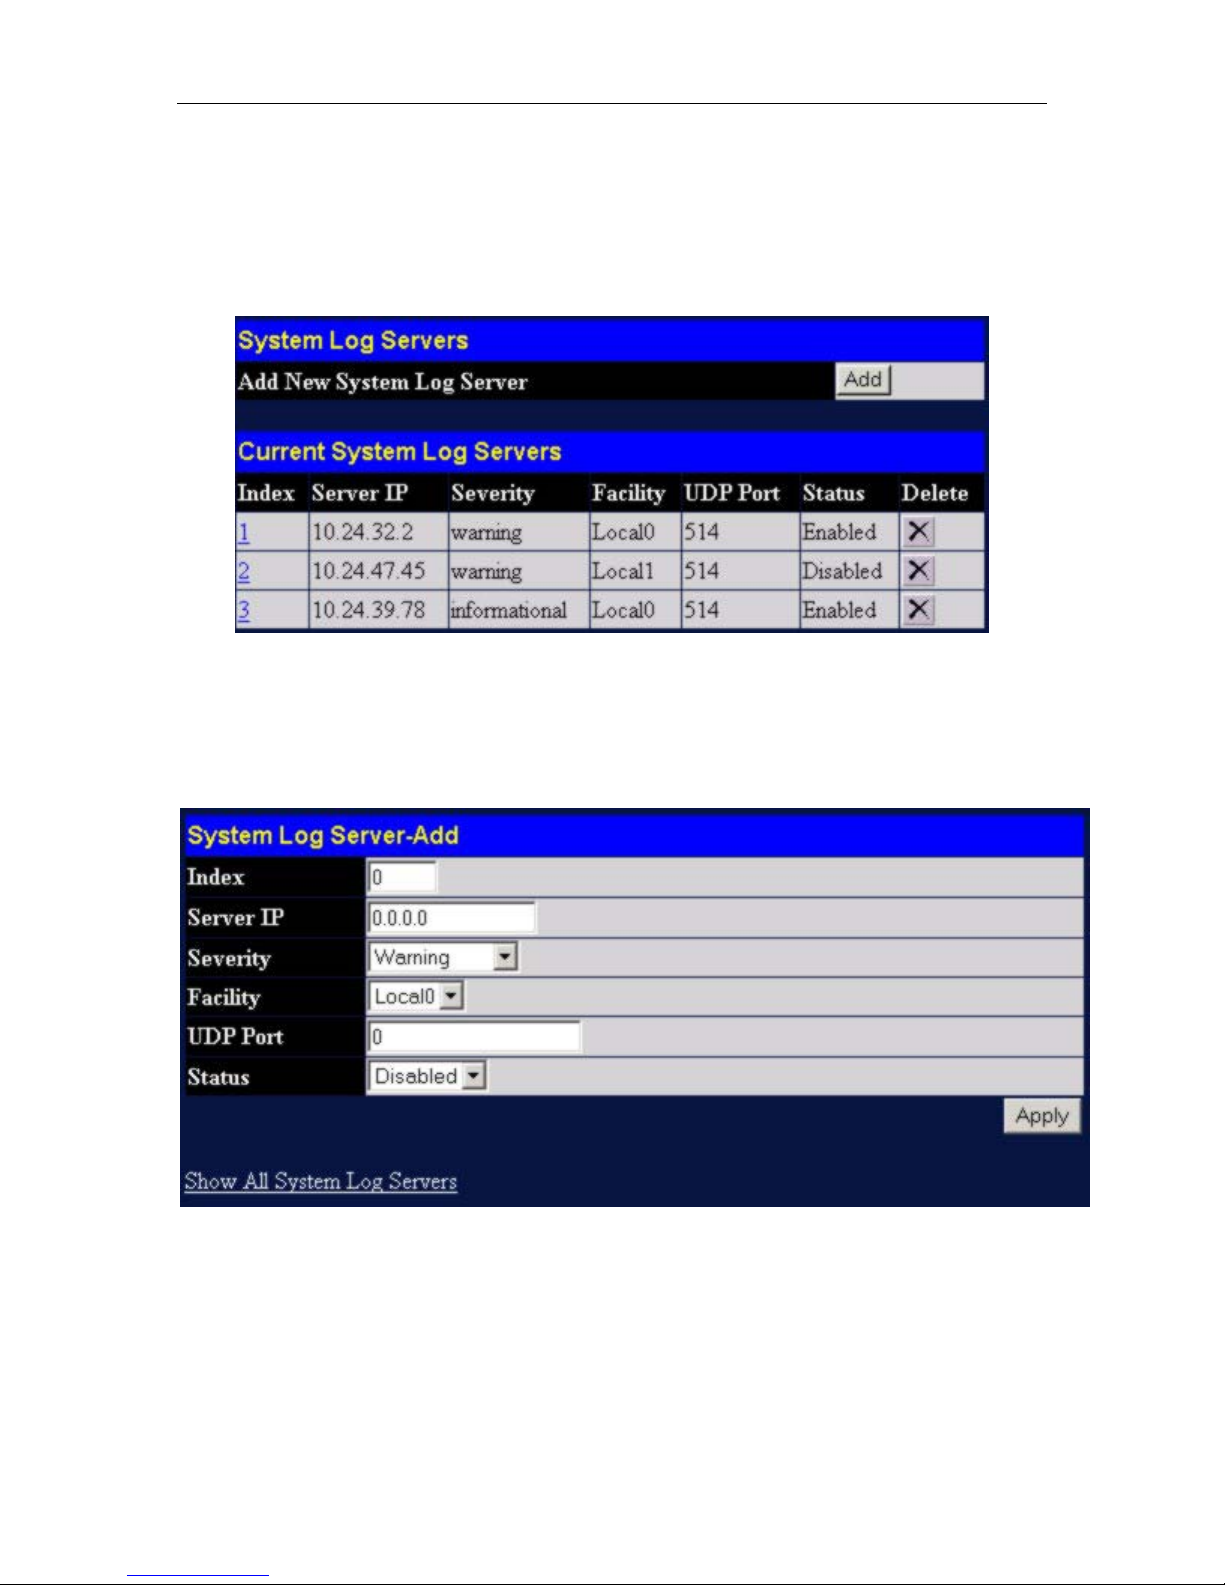
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
System Log Server
Use the System Log to keep a record of warning and other pertinent system information.
The Switch can send system log (SysLog) messages to up to four designated servers.
Figure 4- 34. System Log Servers entries table
Click the Add button to bring up the window pictured below. The parameters configured for adding System
Log are described in the table below. To eliminate a System Log Server configuration, click the X in the
Delete column for the configuration being removed.
Figure 4- 35. System Log Servers − Add menu
83
Page 84
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Configure these parameters for the system log:
Parameter Description
Index
Server IP
Severity
Facility
Syslog server settings index (1-4).
The IP address of the Syslog server.
This drop-down menu allows you to select the level of messages that will
be sent. The options are Warning, Informational, and ALL.
Some of the operating system daemons and processes have been
assigned Facility values. Processes and daemons that have not been
explicitly assigned a Facility may use any of the "local use" facilities or they
may use the "user-level" Facility. Those Facilities that have been
designated are shown in the following: Bold font means the facility values
that the Switch currently supports.
Numerical Facility
Code
0 kernel messages
1 user-level messages
2 mail system
3 system daemons
4 security/authorization messages
5 messages generated internally by syslog line printer subsystem
7 network news subsystem
8 UUCP subsystem
9 clock daemon
10 security/authorization messages
11 FTP daemon
12 NTP subsystem
13 log audit
14 log alert
15 clock daemon
16 local use 0 (local0)
17 local use 1 (local1)
18 local use 2 (local2)
19 local use 3 (local3)
20 local use 4 (local4)
21 local use 5 (local5)
22 local use 6 (local6)
23 local use 7 (local7)
UDP Port
Status
Type the UDP port number used for sending Syslog messages.
Choose Enabled or Disabled to activate or deactivate this
84
Page 85
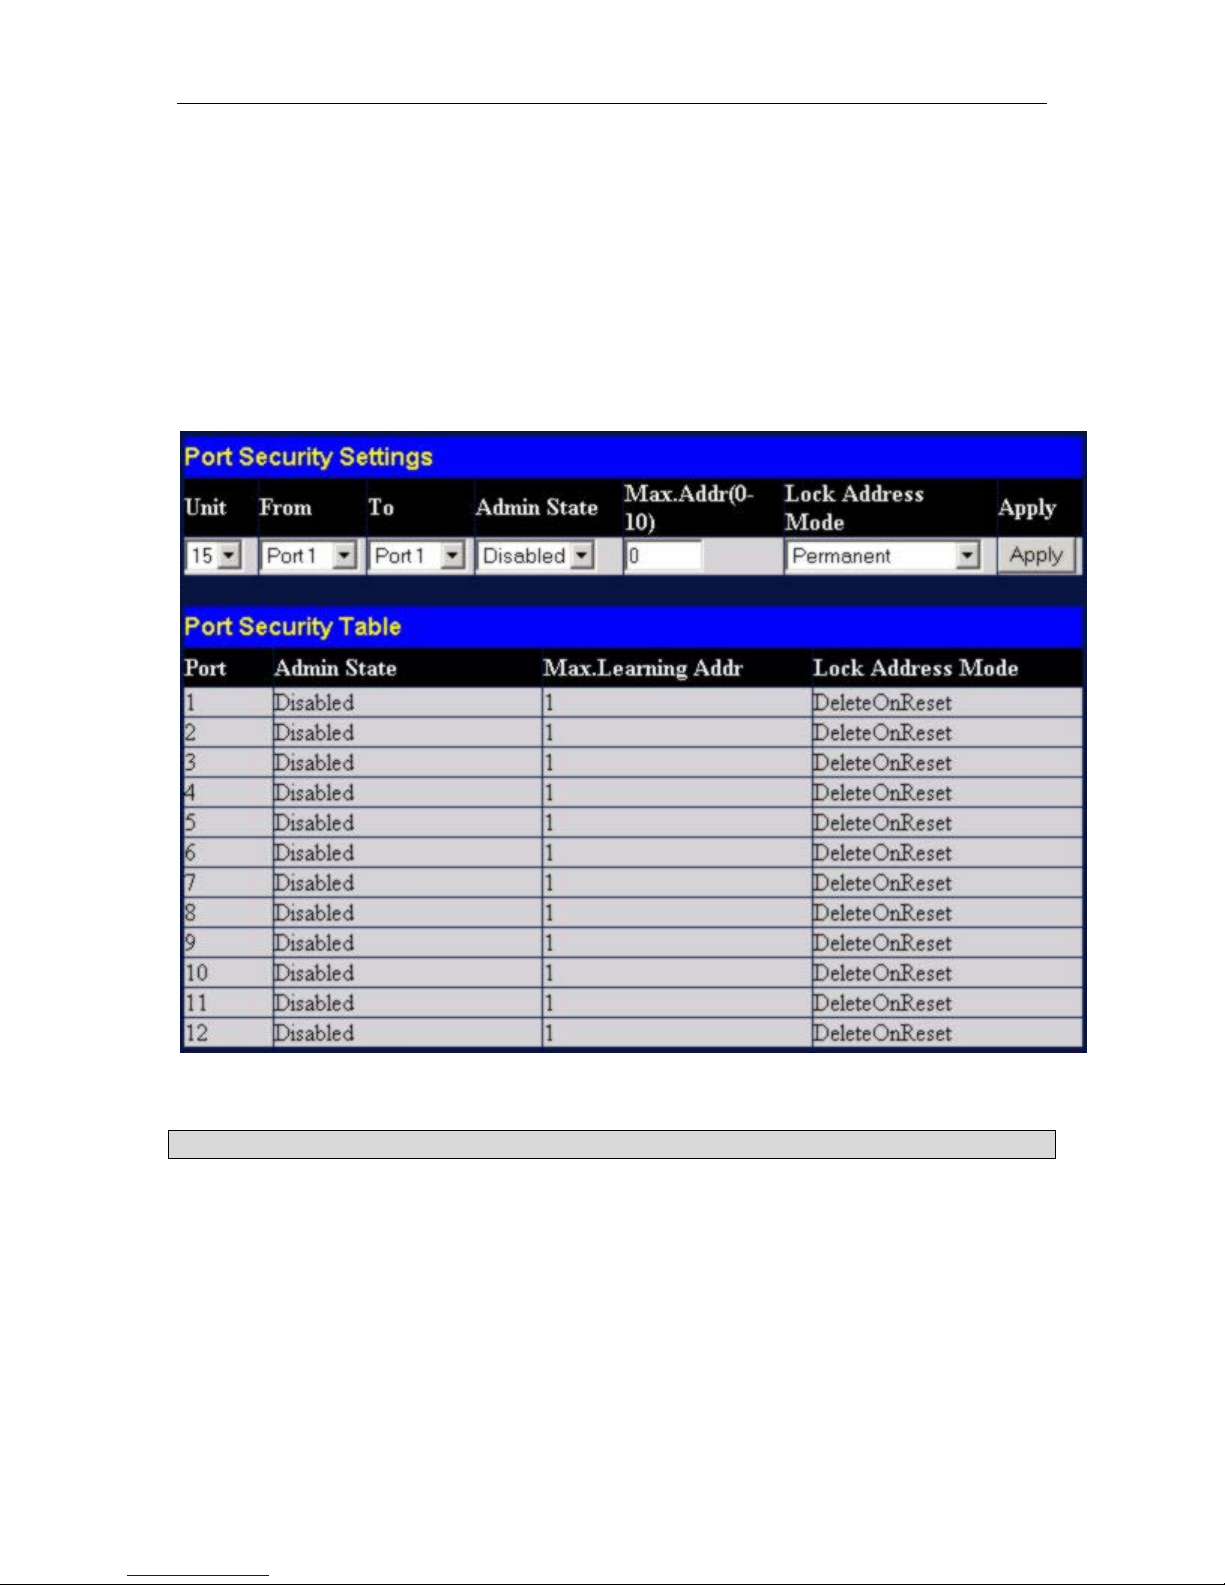
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Port Security
A given port’s (or a range of port’s) dynamic MAC address learning can be locked such that the current
source MAC addresses entered into the MAC address forwarding table can not be changed once the port
lock is enabled. The port can be locked by using the Admin State pull-down menu to Enabled, and clicking
Apply.
This is a security feature that prevents unauthorized computers (with source MAC addresses unknown to
the Switch prior to locking the port (or ports) from connecting to the Switch’s locked ports and gaining
access to the network.
Figure 4- 36. Port Security Settings menu and table
The following parameters can be set:
Parameter Description
Unit
From/To
Admin State
Max.Addr(0-10)
Allows you to specify a Switch in a Switch stack using that Switch’s Unit
ID. The number 15 indicates a Switch in standalone mode.
A consecutive group of ports may be configured starting with the selected
port.
This pull-down menu allows you to enable or disable Port Security (locked
MAC address table for the selected ports.)
The number of MAC addresses that will be in the MAC address forwarding
85
Page 86

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
table for the selected Switch and group of ports.
Lock Address Mode
This pull-down menu allows you to select how the MAC address table
locking will be implemented on the Switch, for the selected group of ports.
The options are Permanent, DeleteOnReset, and DeleteOnTimeout.
SNTP Settings
The Simple Network Time Protocol (SNTP) (an adaptation of the Network Time Protocol (NPT)) is
configured on the Switch using the following windows.
Current Time and SNTP Settings
The following parameters can set or are displayed:
Parameter Description
Current Time
Time Source
SNTP State
SNTP Secondary
Server
SNTP Poll Interval
Displays the current system time.
Displays the time source for the system.
Use this pull-down menu to enable or disable SNTP.
This is the primary server the SNTP information will be taken from
This is the interval between requests for updated SNTP information.
Figure 4- 37. Current Time and SNTP menu
86
Page 87
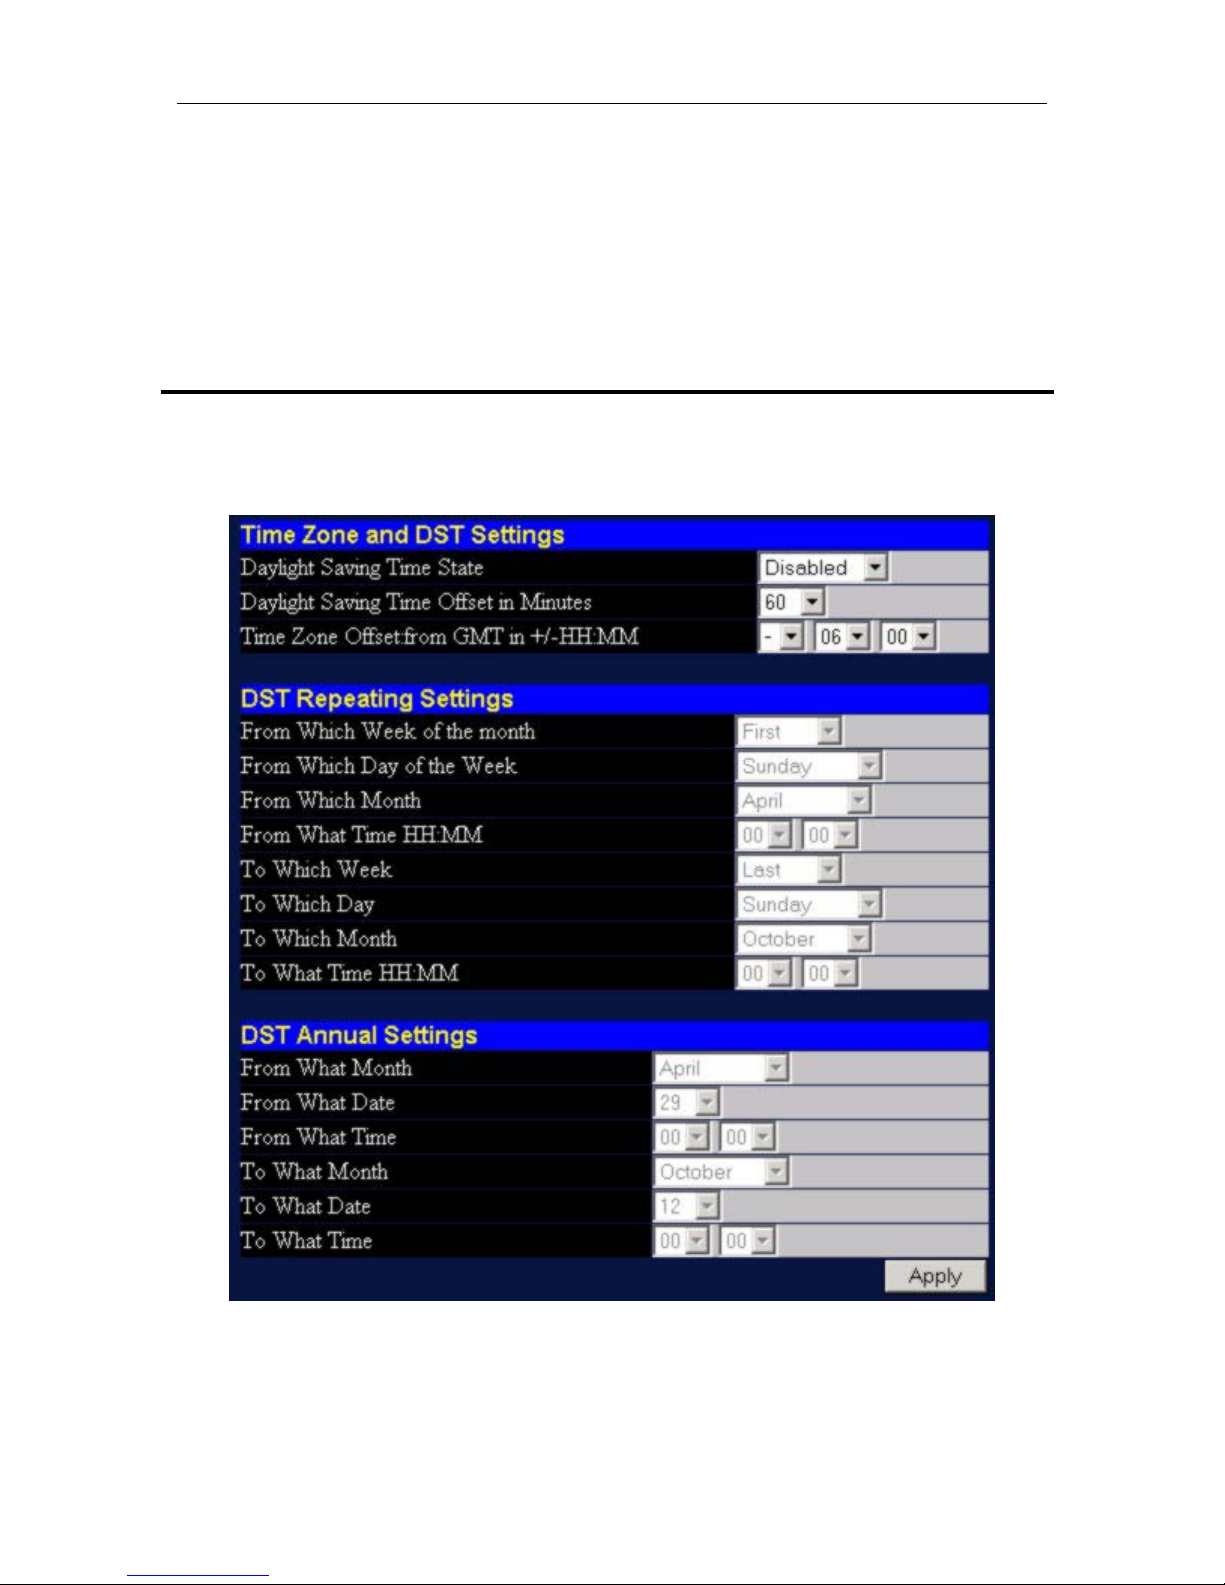
in Seconds
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Year
Month
Day
Time in HH MM SS
Enter the current year, if you want to update the system clock.
Enter the current month, if you want to update the system clock.
Enter the current day, if you want to update the system clock.
Enter the current time in hours, minutes, and seconds, if you want to
update the system clock.
Time Zone and DST
Adjust time zone settings for the Switch. See the table below for a description of the time zone settings.
Figure 4- 38. Time Zone and DST Settings menu
87
Page 88
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The following parameters can set:
Parameter Description
Daylight Saving
Time State
Daylight Saving
Time Offset in
Minutes
Time Zone Offset
from GMT in +/HH:MM
DST Repeating
Settings
From: Which Week
of the month
From: Which Day of
Week
From: Which Month
From: What Time
HH:MM
Use this pull-down menu to enable or disable the DST Settings.
Use this pull-down menu to specify the amount of time that will constitute
your local DST offset − 30, 60, 90, or 120 minutes.
Use these pull-down menus to specify your local time zone’s offset from
Greenwich Mean Time (GMT.)
Repeating - Using repeating mode will enable DST seasonal time
adjustment. Repeating mode requires that the DST beginning and ending
date be specified using a formula. For example, specify to begin DST on
Saturday during the second week of April and end DST on Sunday during
the last week of October.
Enter the week of the month that DST will start.
Enter the day of the week that DST will start on.
Enter the month DST will start on.
Enter the time of day that DST will start on.
To: Which Week
To: Which Day
To: Which Month
To: What Time
HH:MM
DST Annual Settings
From: What Month
From: What Date
From: What Time
To: What Month
To: What Date
Enter the week of the month the DST will end.
Enter the day of the week that DST will end.
Enter the month that DST will end.
Enter the time DST will end.
Annual - Using annual mode will enable DST seasonal time adjustment.
Annual mode requires that the DST beginning and ending date be
specified concisely. For example, specify to begin DST on April 3 and end
DST on October 14.
Enter the month DST will start on, each year.
Enter the day of the week DST will start on, each year.
Enter the time of day DST will start on, each year.
Enter the month DST will end on, each year.
Enter the day of the week DST will end on, each year.
88
Page 89
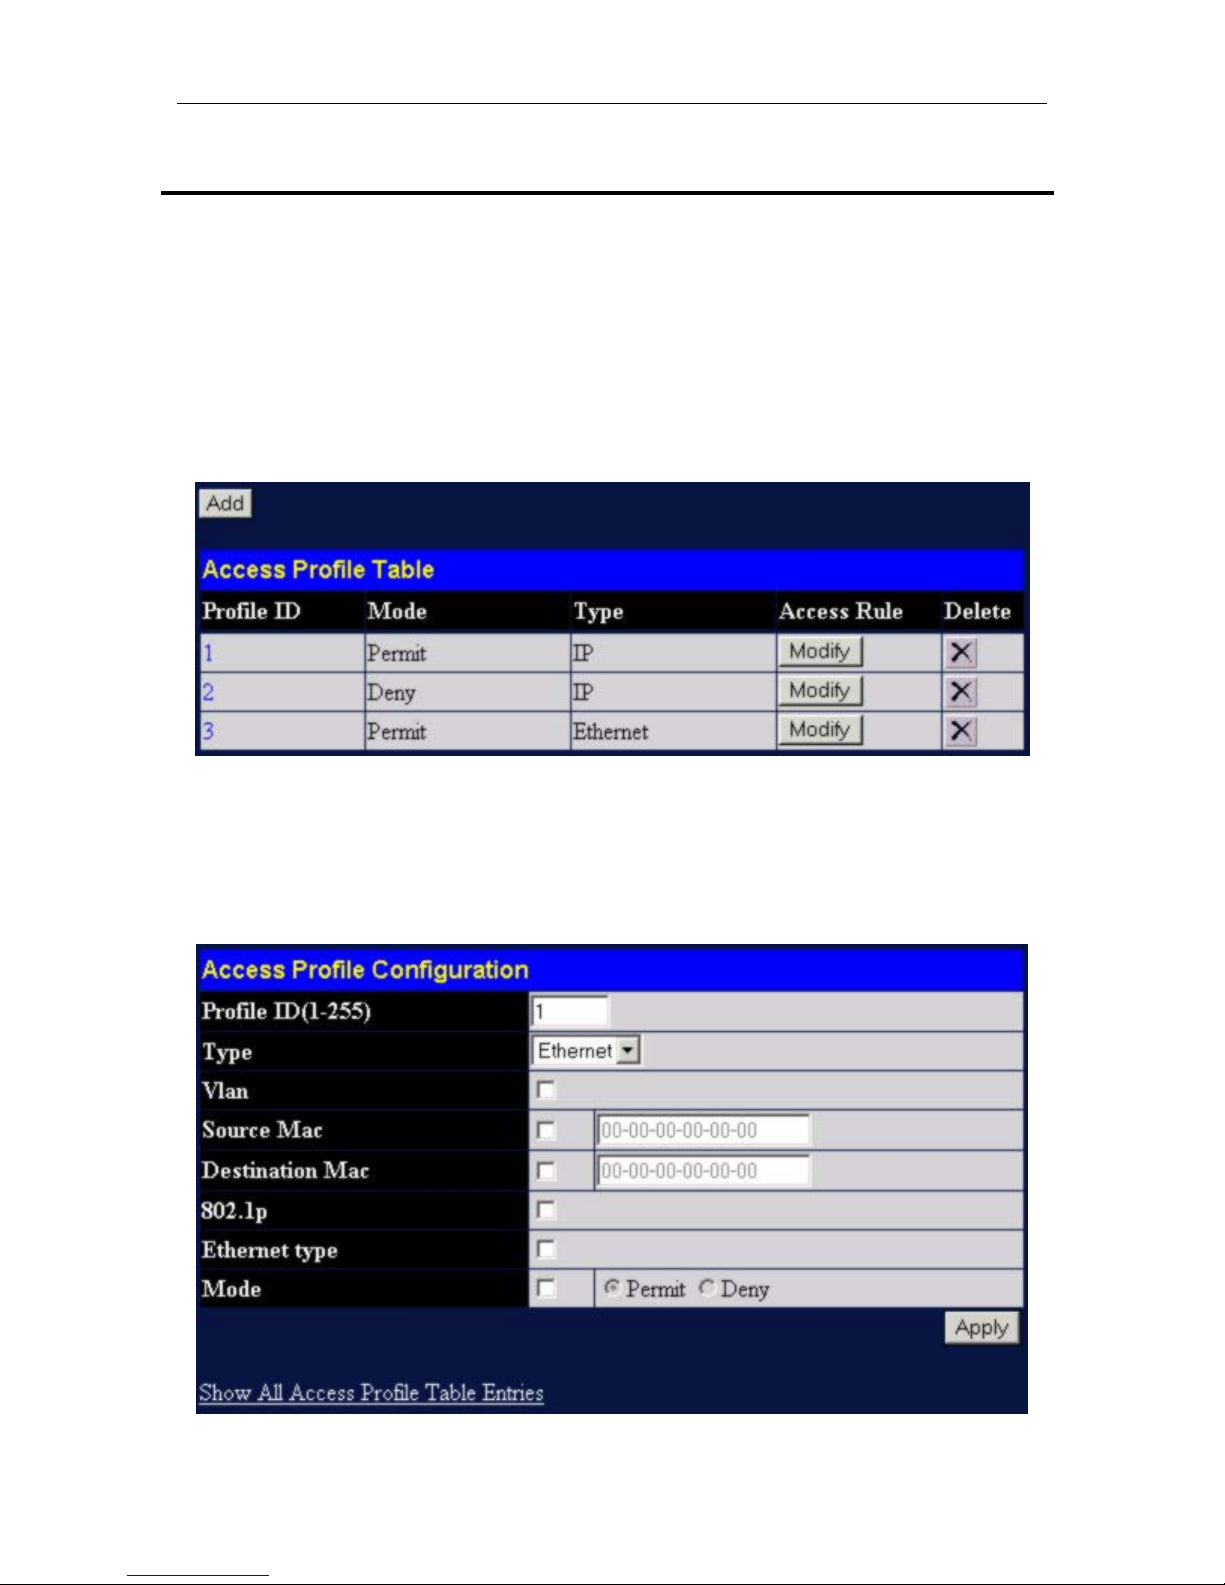
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
To: What Time
Enter the time of day that DST will end on, each year.
Access Profile Table
Access profiles allow you to establish criteria to determine whether or not the Switch will forward packets
based on the information contained in each packet’s header. These criteria can be specified on a basis of
VLAN, MAC address or IP address.
Creating an access profile is divided into two basic parts. The first is to specify which part or parts of a
frame the Switch will examine, such as the MAC source address or the IP destination address. The second
part is entering the criteria the Switch will use to determine what to do with the frame. The entire process is
described below in two parts.
To display the currently configured Access Profiles on the Switch, open the Configuration folder and click
on the Access Profile Table link. This will open the Access Profile Table window, as shown below.
Figure 4- 39. Access Profile Table window
To add an entry to the Access Profile Table window, click the Add button. This will open the Access
Profile Configuration window, as shown below. There are two Access Profile Configuration windows −
one for Ethernet (or MAC address-based) profile configuration and one for IP address-based profile
configuration. You can Switch between the two Access Profile Configuration windows by using the Type
drop-down menu, and clicking on the Apply button. The Access Profile Configuration window for
Ethernet is shown below.
89
Page 90

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 40. Access Profile Configuration (Ethernet) menu
The following parameters can be set for Ethernet type Access Profile configurations:
Parameter Description
Profile ID(1-255)
Type
Vlan
Source Mac
Destination Mac
802.1p
Ethernet type
Type in a unique identifier number for this profile set or allow an ID to be
automatically assigned by checking the Auto Assign option. This value
can be set from 1 to 255.
Select profile based on Ethernet (MAC Address) or IP address. This will
change the window according to the requirements for the type of profile.
Select Ethernet to instruct the Switch to examine the layer 2 part of each
packet header. Select IP to instruct the Switch to examine the IP address
in each frame’s header.
Selecting this option instructs the Switch to examine the VLAN part of
each packet header and use this as the, or part of the criterion for
forwarding.
Source MAC Mask - Enter a MAC address mask for the source MAC
address.
Destination MAC Mask - Enter a MAC address mask for the destination
MAC address.
Selecting this option instructs the Switch to examine the 802.1p priority
value of each packet header and use this as the, or part of the criterion
for forwarding.
Selecting this option instructs the Switch to examine the Ethernet type
value of each packet header and use this as the, or part of the criterion
for forwarding.
Mode
Select Permit to specify that the packets that match the access profile are
forwarded by the Switch, according to any additional rule added (see
below).
Select Deny to specify that packets that do not match the access profile
are not forwarded by the Switch and will be filtered.
The page shown below is the Access Profile Configuration menu for IP.
90
Page 91
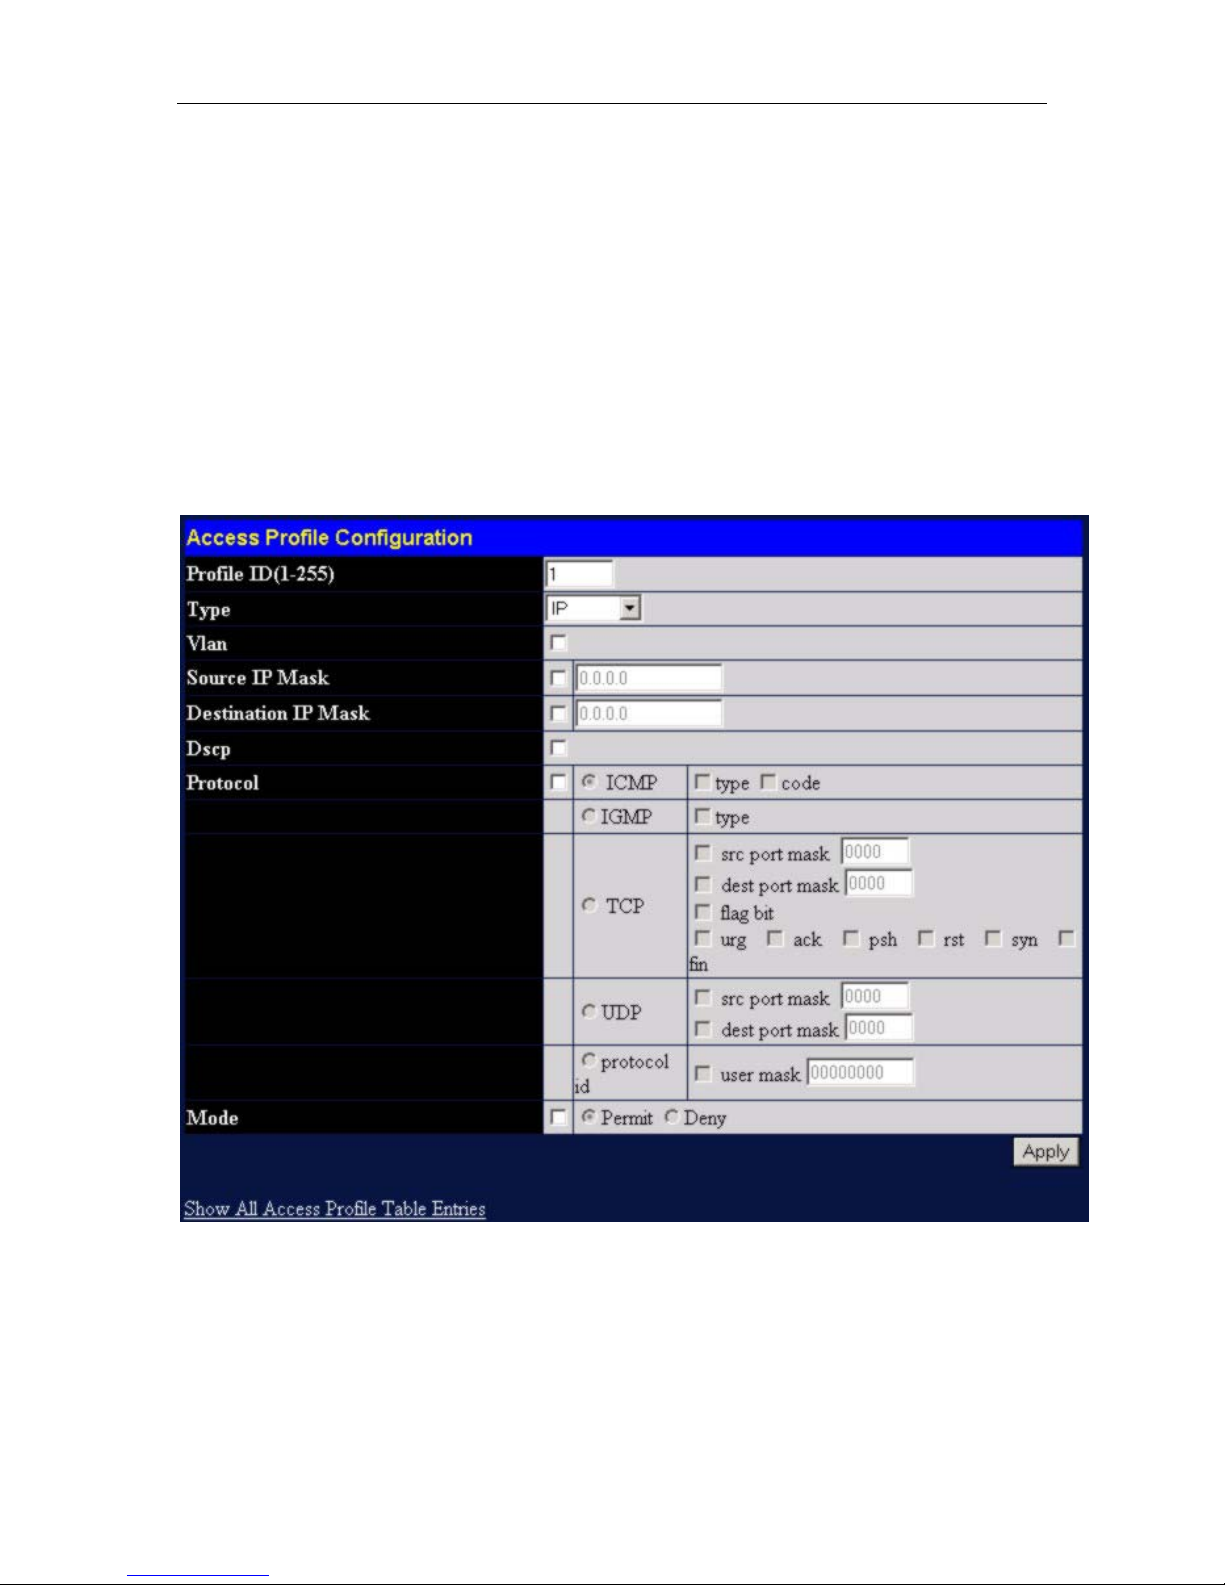
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
IP based Access Profile configurations use a different parameters set. See the table below for a description
of the various settings.
Figure 4- 41. Access Profile Configuration (IP) window
91
Page 92

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The following parameters can be set:
Parameter Description
Type in a unique identifier number for this profile set or allow an ID to be
Profile ID(1-255)
automatically assigned by checking the Auto Assign option. This value
can be set from 1 to 255.
Select profile based on Ethernet (MAC Address) or IP address. This will
change the menu according to the requirements for the type of profile.
Type
Select Ethernet to instruct the Switch to examine the layer 2 part of each
packet header. Select IP to instruct the Switch to examine the IP address
in each frame’s header.
Selecting this option instructs the Switch to examine the VLAN part of
Vlan
each packet header and use this as the, or part of the criterion for
forwarding.
Source IP Mask
Destination IP Mask
Source IP Mask - Enter an IP address mask for the source IP address.
Destination IP Mask - Enter an IP address mask for the destination MAC
address.
Selecting this option instructs the Switch to examine the DiffServ Code
Dscp
part of each packet header and use this as the, or part of the criterion for
forwarding.
Selecting this option instructs the Switch to examine the protocol type
value in each frame’s header. You must then specify what protocol(s) to
include according to the following guidelines:
Select ICMP to instruct the Switch to examine the Internet Control
Message Protocol (ICMP) field in each frame’s header.
Select type to further specify that the access profile will apply an ICMP
type value, or specify code to further specify that the access profile will
apply an ICMP cod value.
Select IGMP to instruct the Switch to examine the Internet Group
Management Protocol (ICMP) field in each frame’s header.
Select type to further specify that the access profile will apply an IGMP
type value
Select TCP to use the TCP port number contained in an incoming packet
as the forwarding criterion. Selecting TCP requires that you specify a
Protocol
source port mask, a destination port mask or a flag bite.
src port mask − Specify a TCP port mask for the source port in hex form
(hex 0x0-0xffff).
dest port mask − Specify a TCP port mask for the destination port in hex
form (hex 0x0-0xffff).
flag bite – Specify a flag bite in the TCP header.
Select UDP to use the UDP port number contained in an incoming packet
as the forwarding criterion. Selecting UDP requires that you specify a
source port mask and/or a destination port mask.
src port mask − Specify a TCP port mask for the source port in hex form
(hex 0x0-0xffff).
dest port mask − Specify a TCP port mask for the destination port in hex
form (hex 0x0-0xffff).
protocol id − Specify a TCP port mask for the destination port in hex form
(hex 0x0-0xffffffff).
Mode
Select Permit to specify that the packets that match the access profile are
92
Page 93

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
forwarded by the Switch, according to any additional rule added (see
below).
Select Deny to specify that packets that do not match the access profile
are not forwarded by the Switch and will be filtered.
To establish the rule for a previously created Access Profile, select the Access Profile entry from the
Access Profile Table window and then click the Modify button for that individual entry.
Figure 4- 42. Access Rule Table window
To create a new rule set for the access profile, click the Add button. Click on View to see the settings for
the rule entry. A new window is displayed. To remove a previously created rule, select it and click the
Delete button.
Figure 4- 43. Access Rule Configuration (Ethernet) menu
Configure the Access Rule Configuration settings and click the Apply button to enter it in the Access Rules
table. See the table below for a description of the rule parameters.
93
Page 94
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
The following parameters can be set:
Parameter Description
Profile ID
Access ID
Type
Priority(0-7)
Replace Dscp(0-63)
Vlan Name
Source Mac
Destination Mac
This is the identifier number for this profile set.
Type in a unique identifier number for this access. This value can be set
from 1 to 255.
Select profile based on Ethernet (MAC Address) or IP address. This will
change the menu according to the requirements for the type of profile.
Select Ethernet to instruct the Switch to examine the layer 2 part of each
packet header. Select IP to instruct the Switch to examine the IP address
in each frame’s header.
Specify the priority tag, located in the packet header that will be identified
by the Switch.
Select this option to instruct the Switch to replace the DSCP value (in a
packet that meets the selected criteria) with the value entered in the
adjacent field.
Allows the entry of a name for a previously configured VLAN.
Source MAC Address - Enter a MAC Address for the source MAC
address.
Destination MAC Address - Enter a MAC Address mask for the
destination MAC address.
802.1p(0-7)
Ethernet Type
Enter a value from 0 to 7 to specify that the access profile will apply only
to packets with this 802.1p priority value.
Specifies that the access profile will apply only to packets with this
hexadecimal 802.1Q Ethernet type value (hex 0x0-0xffff) in the packet
header. The Ethernet type value may be set in the form: hex 0x0-0xffff,
which means the user may choose any combination of letters and
numbers ranging from a-f and from 0-9999.
94
Page 95

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 44. Access Rule Configuration (IP) window
Configure the Access Rule Configuration settings on the window above.
The following parameters can be set:
Parameter Description
Profile ID
Access ID
This is the identifier number for this profile set.
Type in a unique identifier number for this access. This value can be set
from 1 to 255.
Type
Select profile based on Ethernet (MAC Address) or IP address. This will
change the menu according to the requirements for the type of profile.
Select Ethernet to instruct the Switch to examine the layer 2 part of each
packet header. Select IP to instruct the Switch to examine the IP address
in each frame’s header.
Priority(0-7)
Specify the priority tag, located in the packet header that will be identified
by the Switch.
Select this option to instruct the Switch to replace the DSCP value (in a
Dscp(0-63)
packet that meets the selected criteria) with the value entered in the
adjacent field.
Vlan Name
Source IP
Destination IP
Allows the entry of a name for a previously configured VLAN.
Source IP Address - Enter an IP Address mask for the source IP address.
Destination IP Address- Enter an IP Address mask for the destination IP
address.
This field allows the user to enter a DSCP value in the space provided,
Dscp(0-63)
which will instruct the Switch to examine the DiffServ Code part of each
packet header and use this as the, or part of the criterion for forwarding.
The user may choose a value between 0 and 63.
This field allows the user to modify the protocol used to configure the
Protocol
Access Rule Table window; depending on which protocol the user has
chosen in the Access Profile Table window.
95
Page 96

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
96
Page 97

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Chapter 5
Security Management
Trusted Host
Port Access Entity
802.1X Authenticator Settings
PAE System Control
802.1X Capability Settings
Initialize Port(s)
Reauthenticate Port(s)
Radius Server
Trusted Host
The Security IP Management window allows you to specify the IP addresses of management stations
(PCs) on your network that will be allowed to access the Switch’s Web-based management agent.
You can enter up to three IP addresses of local hosts (on the same subnet as the Switch) that will be
allowed to manage the Switch. It is recommended that the IP address of the local host that will be used to
manage the Switch be entered here to avoid possible frequent disconnection from the Switch’s Web-based
management agent.
Figure 5- 1. Security IP Management window
The following fields can be set:
Parameter Description
IP1 Access to
Switch
IP2 Access to
Switch
IP3 Access to
Switch
Enter the IP address of a management station that will be used to
manage the Switch. This IP address must be on the same subnet as the
Switch.
Enter the IP address of a management station that will be used to
manage the Switch. This IP address must be on the same subnet as the
Switch.
Enter the IP address of a management station that will be used to
manage the Switch. This IP address must be on the same subnet as the
Switch.
97
Page 98

LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Port Access Entity
The Switch is an implementation of the server side of IEEE 802.1X-Port Based Network Access Control.
Through this mechanism, users have to be authorized before being able to access the network. See the
following figure:
Figure 4- 45. Typical 802.1X Configuration Prior to User Authentication
Once the user is authenticated, the Switch unblocks the port that is connected to the user as shown in the
next figure.
98
Page 99
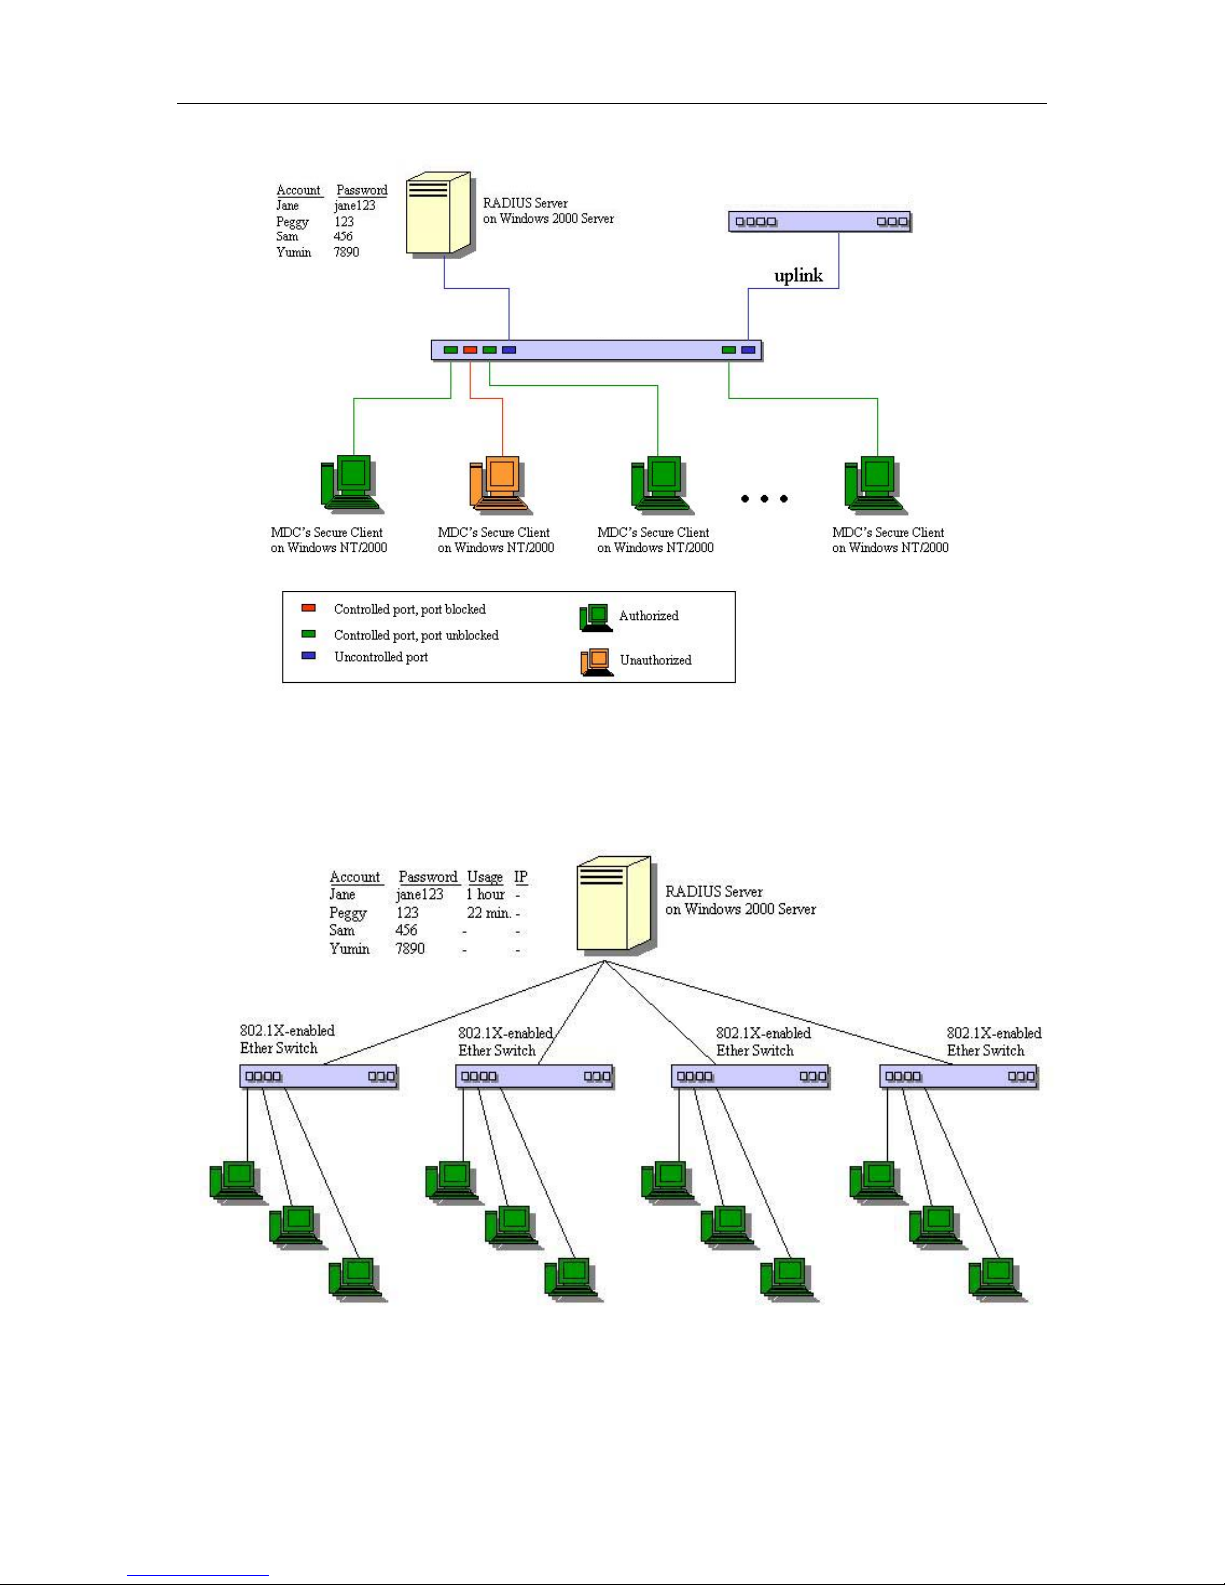
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
Figure 4- 46. Typical 802.1X Configuration with User Authentication
The user’s information, including account number, password, and configuration details such as IP address
and billing information, is stored in a centralized RADIUS server.
Figure 4- 47. Typical Configuration with 802.1X Fully Implemented
99
Page 100
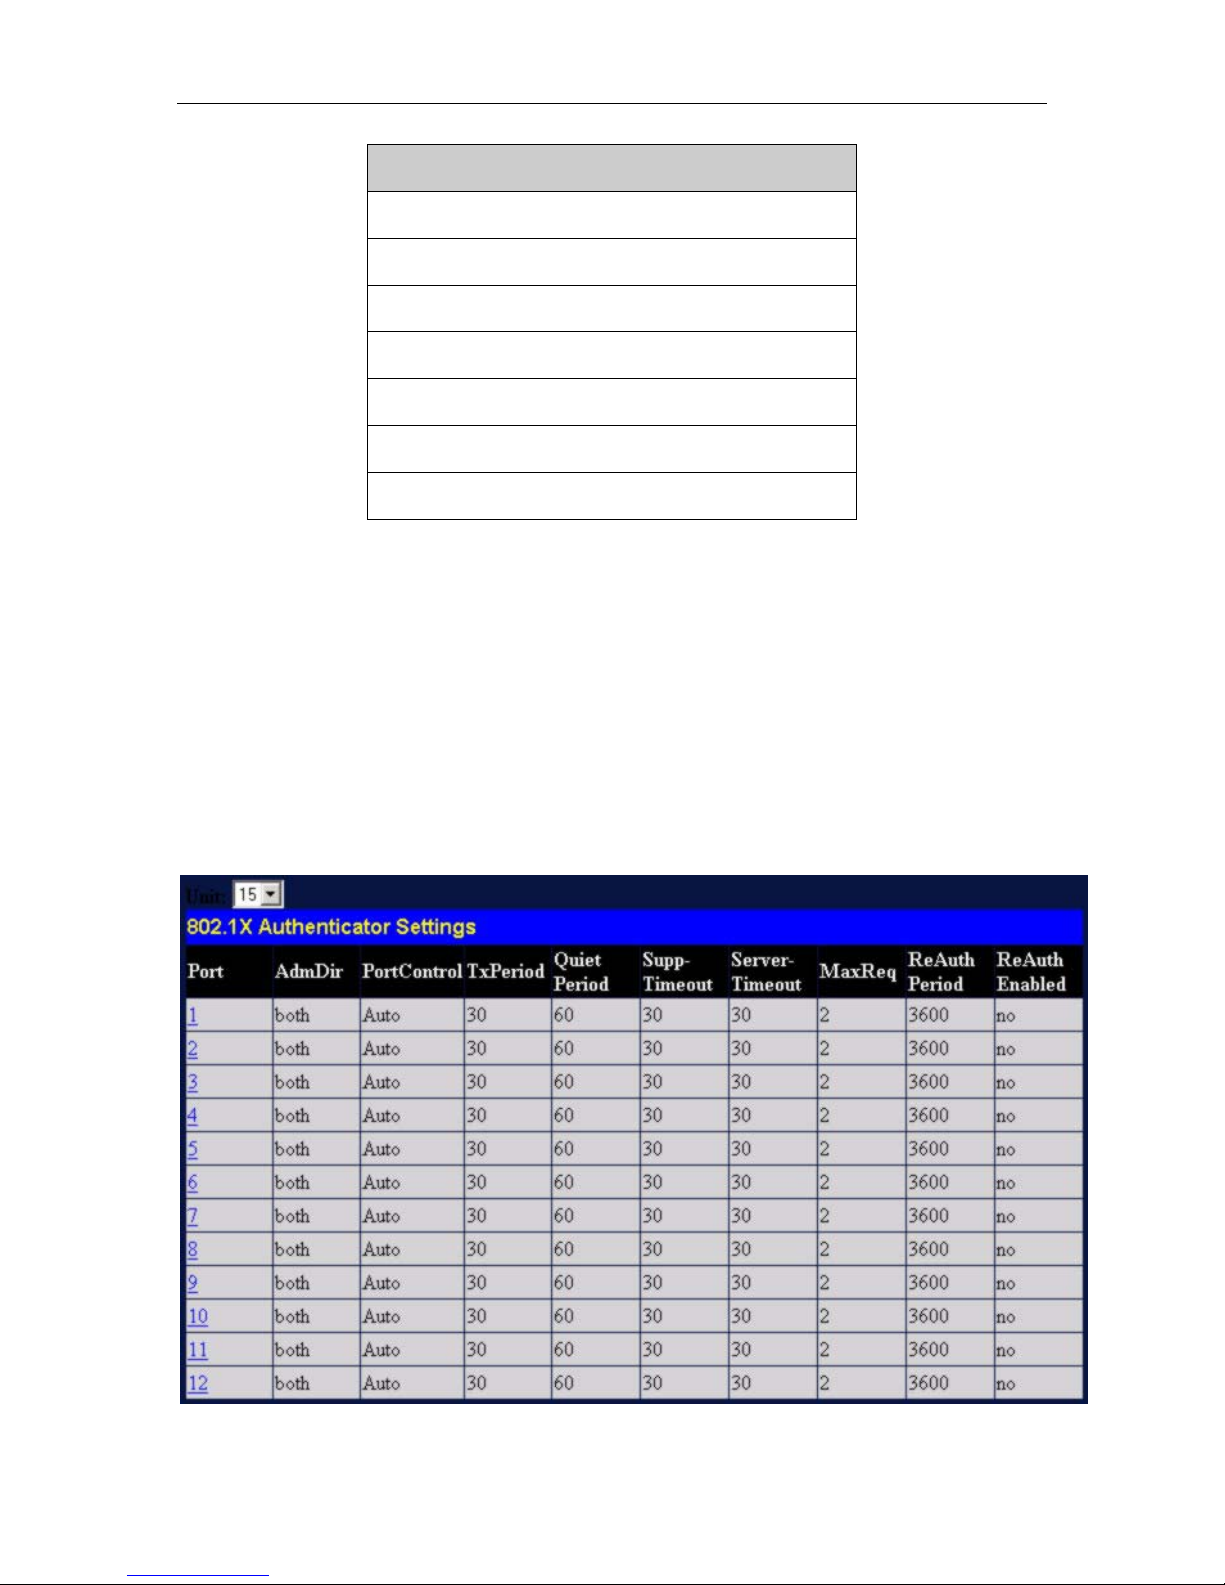
LevelOne GSW-1290 Gigabit Layer2 SNMP Switch
State Machine Name
Port Timers state machine
Authenticator PAE state machine
The Authenticator Key Transmit state machine
Reauthentication Timer state machine
Backend Authentication state machine
Controlled Directions state machine
The Key Receive state machine
Table 4- 2. Conformance to IEEE 802.1X Standards
802.1X Authenticator Settings
To display the current 802.1X Authenticator Settings on the Switch, open the Security folder, and then the
Port Access Entity folder and finally click on the 802.1X Authenticator Settings link:
Figure 4- 48. 802.1X Authenticator Settings entries table
100
 Loading...