

Page 1
IES-2881
24 100FX SFP + 4 GE Combo SFP Managed Switch -40 to 75C
User Manual
v1.00 - 1206
Page 2
User Manual Page 2
Preface
This manual describes how to install and use the Industry Managed Ethernet Switch. This
switch introduced here is designed to deliver full scalability with SNMP/RMON web-based
management functions by providing:
To get the most out of this manual, you should have an understanding of Ethernet
networking concepts.
In this manual, you will find:
Features on the Industry Managed Ethernet Switch
Illustrative LED functions
Installation instructions
Management Configuration
Specifications
Page 3
User Manual Page 3
Table of Contents
PREFACE ....................................................................................................................................................... 2
QUICK START GUIDE ..................................................................................................................................... 5
FUNCTIONAL DESCRIPTION ....................................................................................................................................... 5
PHYSICAL DESCRIPTION ............................................................................................................................................ 6
CONSOLE CONFIGURATION ....................................................................................................................................... 7
WEB CONFIGURATION ............................................................................................................................................. 9
PRODUCT OVERVIEW ................................................................................................................................. 10
INDUSTRY MANAGED ETHERNET SWITCH ................................................................................................................... 10
PACKAGE CONTENTS .............................................................................................................................................. 10
PRODUCT HIGHLIGHTS ........................................................................................................................................... 11
FRONT PANEL DISPLAY ........................................................................................................................................... 13
PHYSICAL PORTS ................................................................................................................................................... 14
SWITCH MANAGEMENT ......................................................................................................................................... 15
INSTALLATION ............................................................................................................................................ 16
SELECTING A SITE FOR THE SWITCH ........................................................................................................................... 16
CONNECTING TO POWER ........................................................................................................................................ 16
CONNECTING TO YOUR NETWORK ............................................................................................................................ 18
SWITCH MANAGEMENT ............................................................................................................................. 19
MANAGEMENT ACCESS OVERVIEW ........................................................................................................................... 19
ADMINISTRATION CONSOLE (CLI) ............................................................................................................................ 20
WEB MANAGEMENT ............................................................................................................................................. 21
SNMP-BASED NETWORK MANAGEMENT ................................................................................................................. 21
PROTOCOLS ......................................................................................................................................................... 21
MANAGEMENT ARCHITECTURE ................................................................................................................................ 22
WEB-BASED BROWSER MANAGEMENT ...................................................................................................... 23
SNMP & RMON MANAGEMENT ................................................................................................................. 24
OVERVIEW ........................................................................................................................................................... 24
SNMP AGENT AND MIB-2 (RFC 1213) .................................................................................................................. 24
RMON MIB (RFC 2819) & BRIDGE MIB (RFC 1493) .............................................................................................. 25
WEB-BASED BROWSER MANAGEMENT ...................................................................................................... 27
LOGGING ON TO THE SWITCH ................................................................................................................................... 27
UNDERSTANDING THE BROWSER INTERFACE ............................................................................................................... 28
SYSTEM ............................................................................................................................................................... 30
PORT .................................................................................................................................................................. 38
SWITCHING .......................................................................................................................................................... 43
TRUNKING ........................................................................................................................................................... 47
STP / RING ......................................................................................................................................................... 48
VLAN ................................................................................................................................................................ 57
QOS ................................................................................................................................................................... 62
SNMP ............................................................................................................................................................... 65
802.1X .............................................................................................................................................................. 69
OTHER PROTOCOLS ............................................................................................................................................... 72
COMMAND LINE CONSOLE MANAGEMENT ................................................................................................ 76
ADMINISTRATION CONSOLE .................................................................................................................................... 76
SYSTEM ............................................................................................................................................................... 89
Page 4
User Manual Page 4
PORT .................................................................................................................................................................. 96
SWITCHING ........................................................................................................................................................ 101
TRUNKING ......................................................................................................................................................... 106
STP / RING ....................................................................................................................................................... 107
VLAN .............................................................................................................................................................. 120
QOS ................................................................................................................................................................. 126
SNMP ............................................................................................................................................................. 129
802.1X ............................................................................................................................................................ 138
OTHER PROTOCOLS ............................................................................................................................................. 143
SPECIFICATIONS ........................................................................................................................................ 154
APPENDIX A .............................................................................................................................................. 155
APPENDIX B .............................................................................................................................................. 156
Page 5
User Manual Page 5
Quick Start Guide
This quick start guide describes how to install and use the Industry Managed Ethernet
Switch. This is the switch of choice for harsh environments constrained by space.
Functional Description
Meets NEMA TS1/TS2 Environmental requirements such as temperature, shock, and
vibration for traffic control equipment.
Meets EN61000-6-2 & EN61000-6-4 EMC Generic Standard Immunity for industrial
environment.
RS-232 console, Telnet, SNMP v1 & v2c & v3, RMON, Web Browser, and TFTP
management.
Supports Command Line Interface in RS-232 console.
Supports 8192 MAC addresses. Provides 3M bits memory buffer.
Supports IEEE802.3/802.3u/802.3ab/802.3z/802.3x. Auto-negotiation:
1000Mbps-full-duplex; 10/100Mbps-full/half-duplex; Auto MDI/MDIX.
100Base-FX: Multi mode SC or ST type, Single mode SC or ST type; 100Base-BX: WDM
Single mode SC type.
1000Base-SX/LX: Multi mode SC type, Single mode SC type; 1000Base-BX: WDM Single
mode SC type.
SFP socket for Gigabit fiber optic expansion.
Store-and-forward mechanism.
Full wire-speed forwarding rate.
AC inlet power socket: 100~240VAC, 50~60Hz internal universal PSU.
Terminal Block power input: +48VDC, -48VDC, 88~370VDC, or 90~264VAC.
Supports redundant power supplies for flexible application.
-40C to 75C (-40℉ to 167℉) operating temperature range.
Tested for functional operation @ -40C to 85C (-40℉ to 185℉).
Industry metal case.
Supports Rack Mounting installation.
Page 6
User Manual Page 6
Physical Description
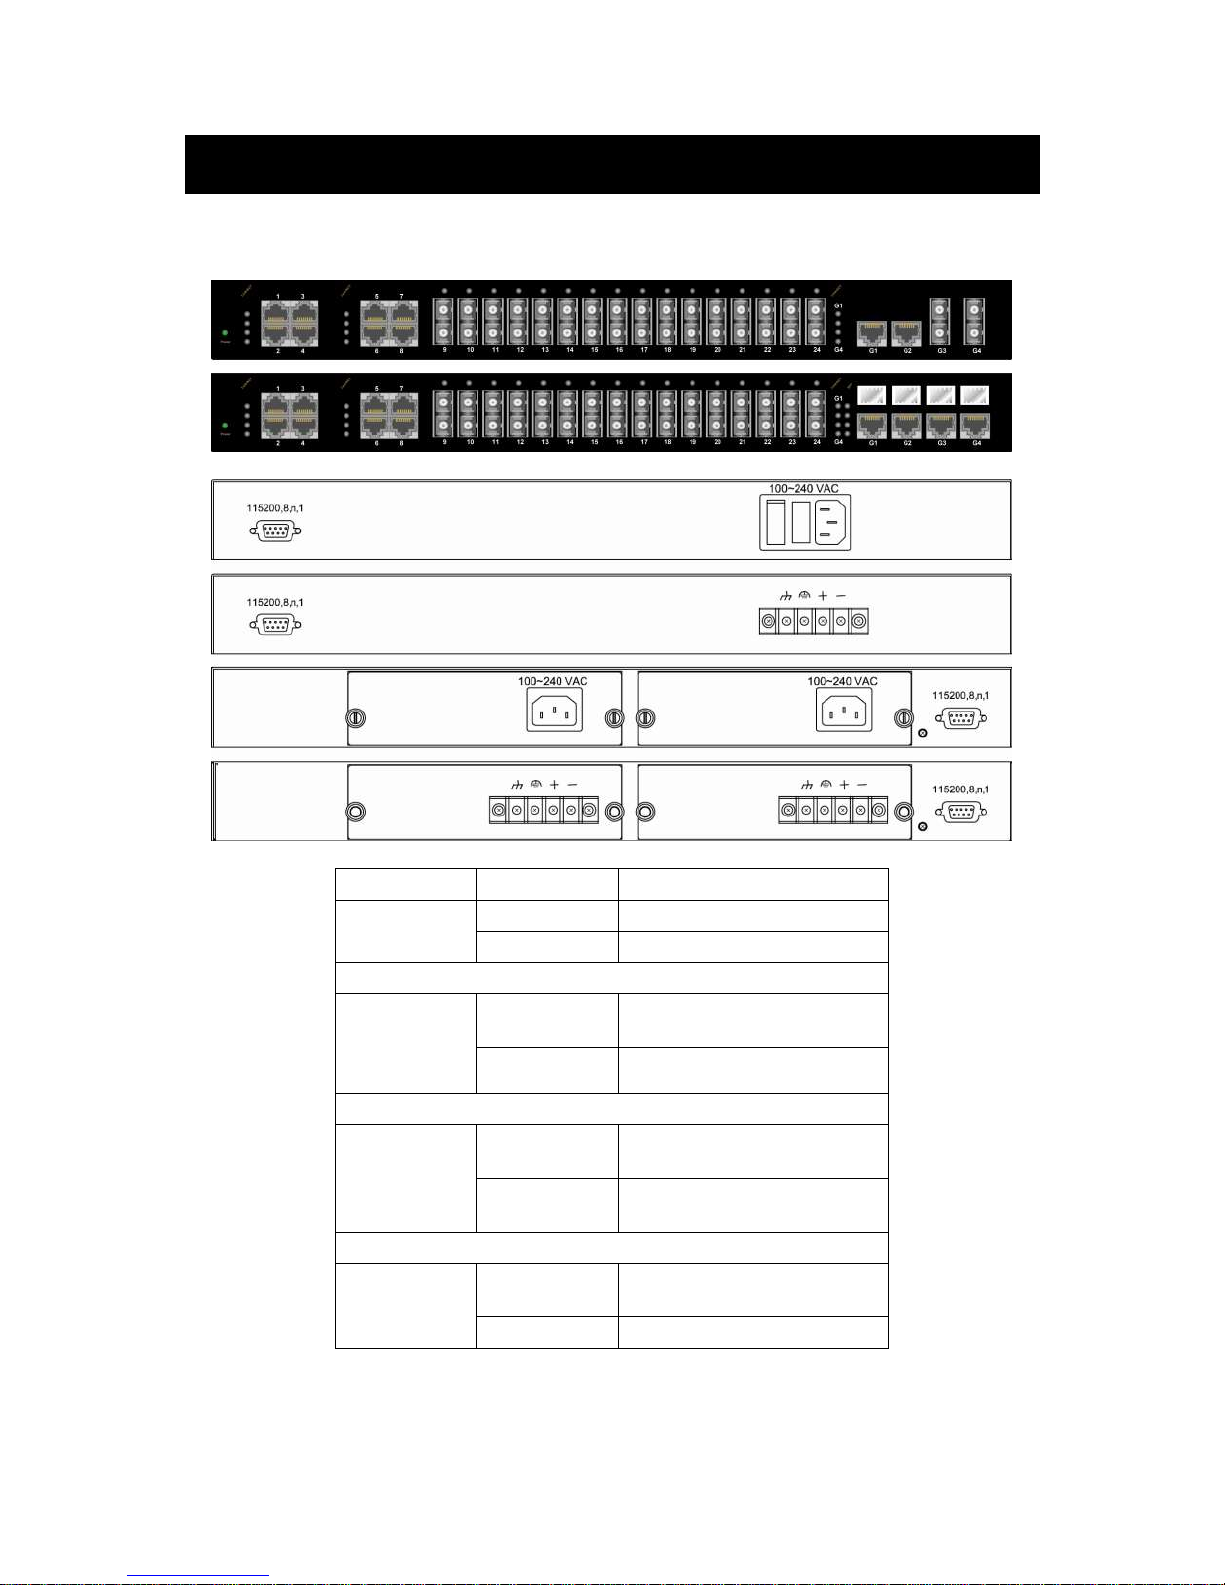
The Port Status LEDs and Power Inputs
LED
State
Indication
Power
Steady
Power on
Off
Power off
10/100Base-TX, 100Base-FX/BX
Link/ACT
Steady
A valid network connection
established
Flashing
Transmitting or receiving data
ACT stands for ACTIVITY
10/100/1000Base-TX, SFP, 1000Base-SX/LX/BX
Link/ACT
Steady
A valid network connection
established
Flashing
Transmitting or receiving data
ACT stands for ACTIVITY
SFP
SFP
Steady
A valid SFP connection
established
Off
Without SFP
Page 7
User Manual Page 7
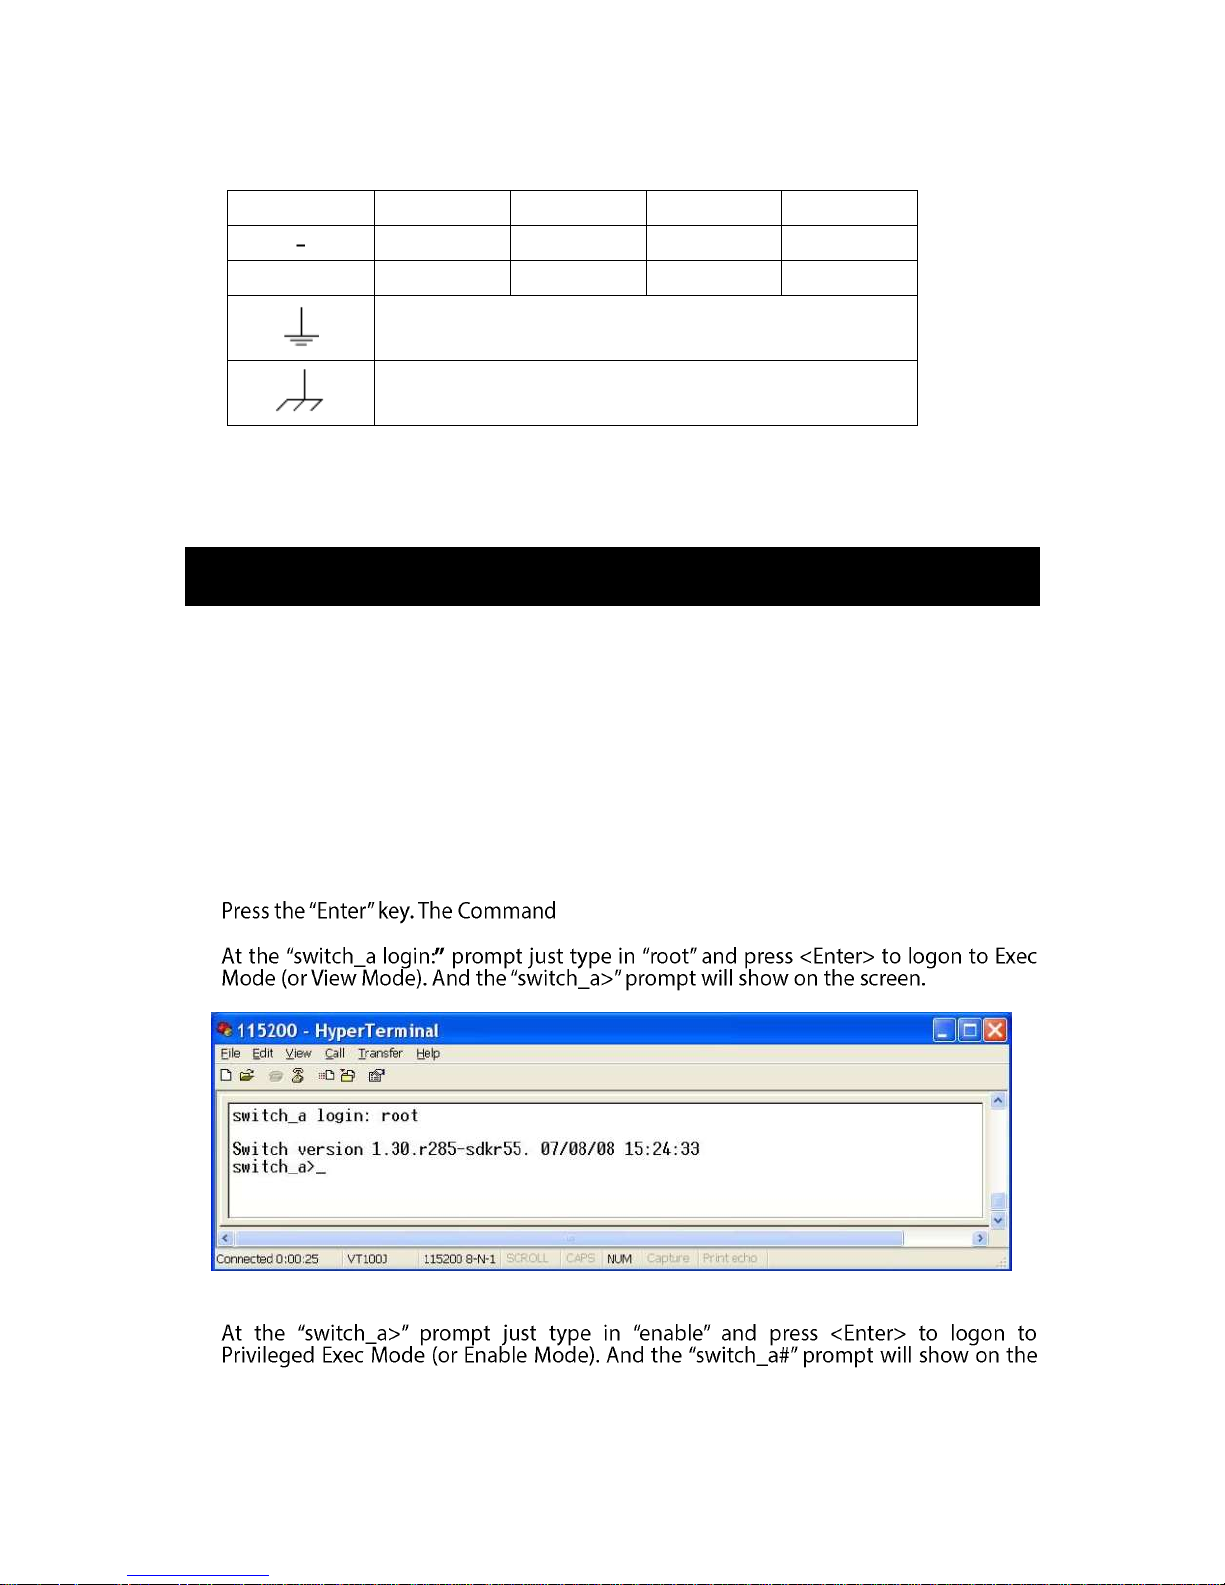
Terminal Block Power Input
+48VDC
-48VDC
88-370VDC
90-264VAC
0
-48 0 N
+
+48
0
88-370
L
Earth Ground
Protect Ground
<Note> Dielectric withstand (Hipot) test for DC power input, must remove metal chip between Earth
Ground and Protect Ground of the terminal block power input to avoid damage to the Switch.
Console Configuration
Connect to the switch console:
Connect the DB9 straight cable to the RS-232 serial port of the device and the RS-232
serial port of the terminal or computer running the terminal emulation application.
Direct access to the administration console is achieved by directly connecting a
terminal or a PC equipped with a terminal-emulation program (such as HyperTerminal)
to the switch console port.
Configuration settings of the terminal-emulation program:
Baud rate: 115,200bps
Data bits: 8
Parity: none
Stop bit: 1
Flow control: none
Line Interface (CLI) screen should appear as below:
Logon to Exec Mode (View Mode):
Logon to Privileged Exec Mode (Enable Mode):
screen.
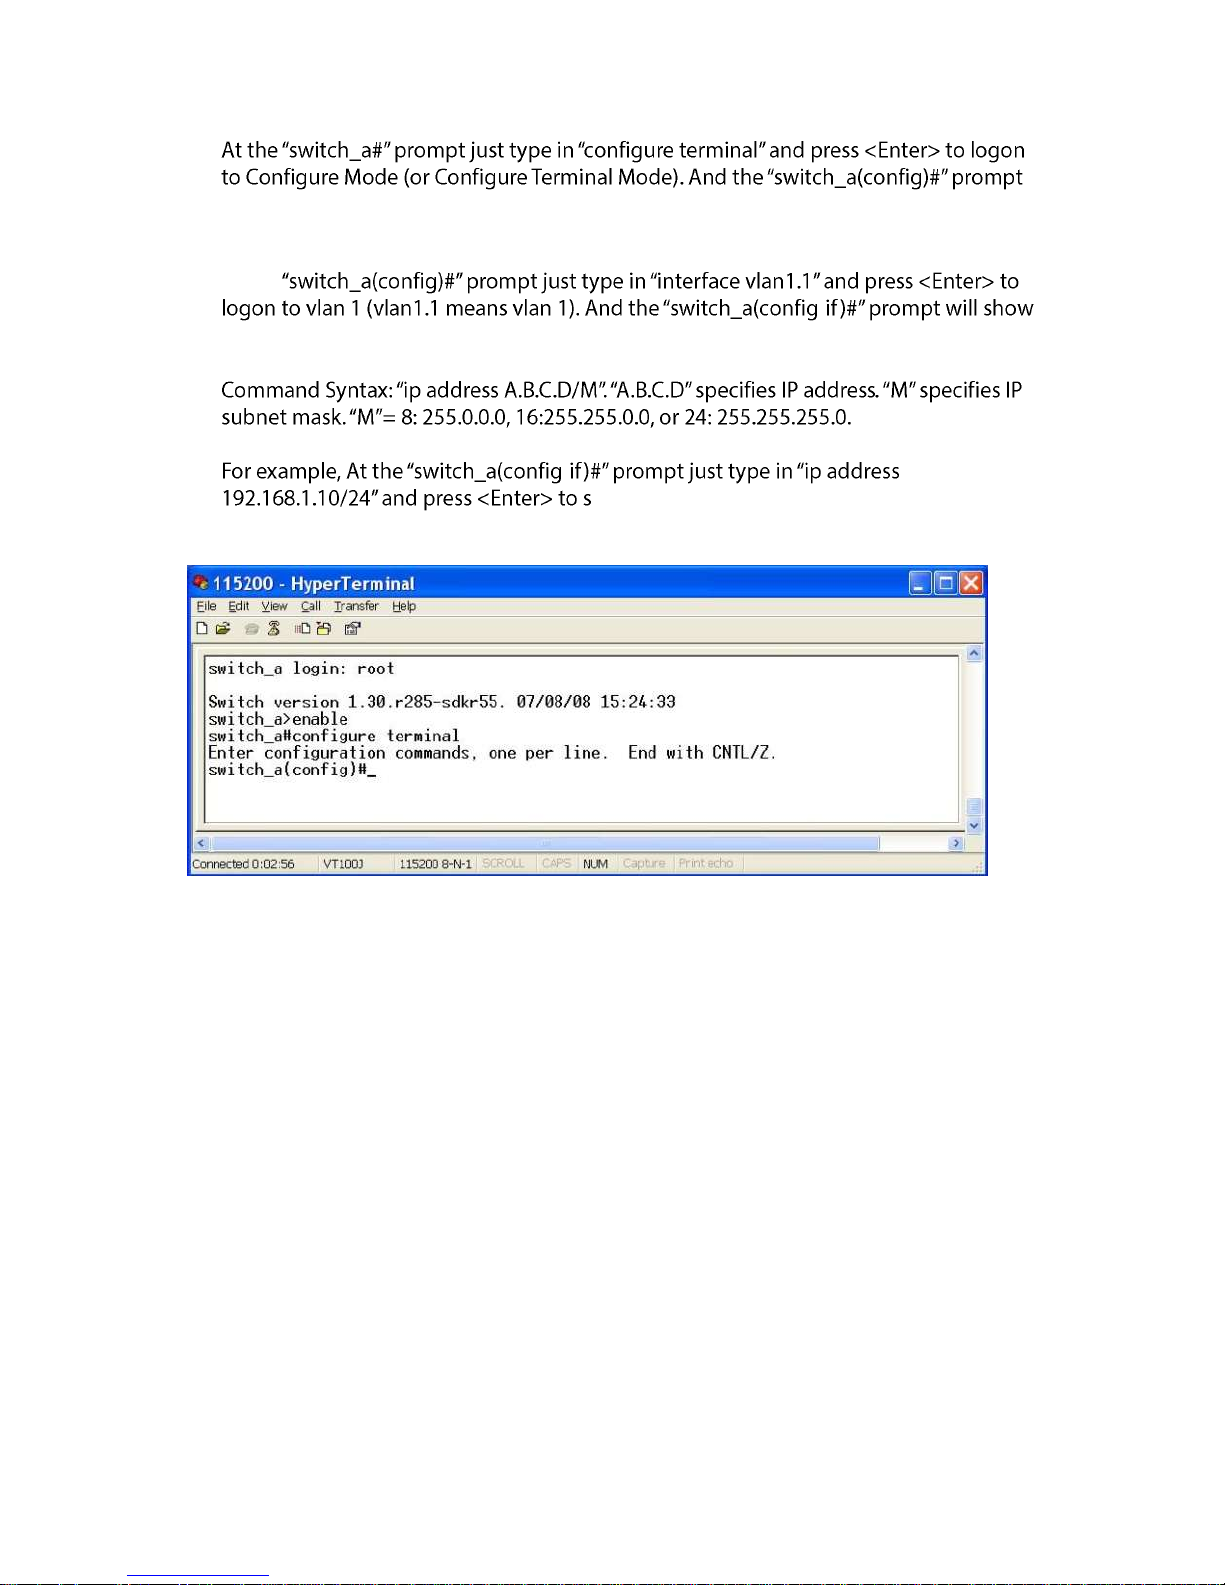
Logon to Configure Mode (Configure Terminal Mode):
Page 8
User Manual Page 8
will show on the screen.
Set new IP address and subnet mask for Switch:
At the
-
on the screen.
et new IP address (192.168.1.10) and new IP
subnet mask (255.255.255.0) for Switch.
Page 9
User Manual Page 9
Web Configuration
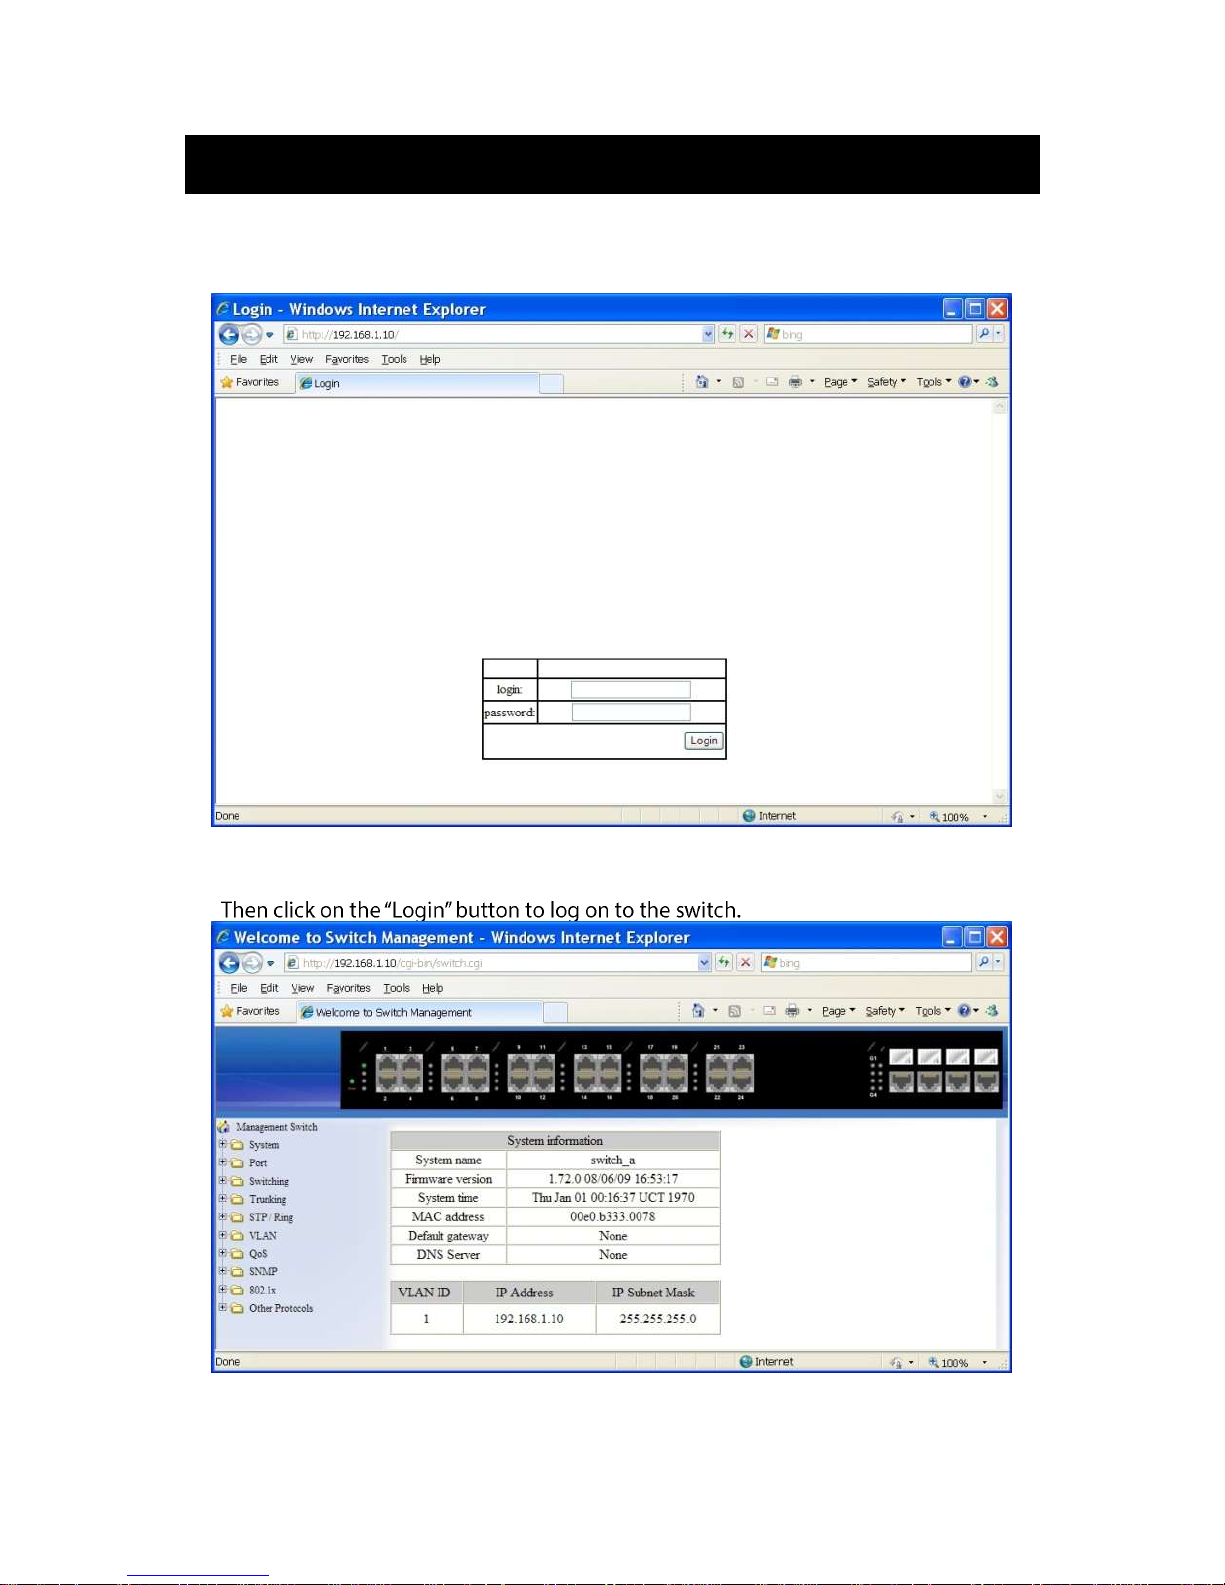
Login the switch:
Specify the default IP address (192.168.1.10) of the switch in the web browser. A login
window will be shown as below:
Enter the factory default login ID: root.
Enter the factory default password (no password).
Page 10
User Manual Page 10
Product Overview
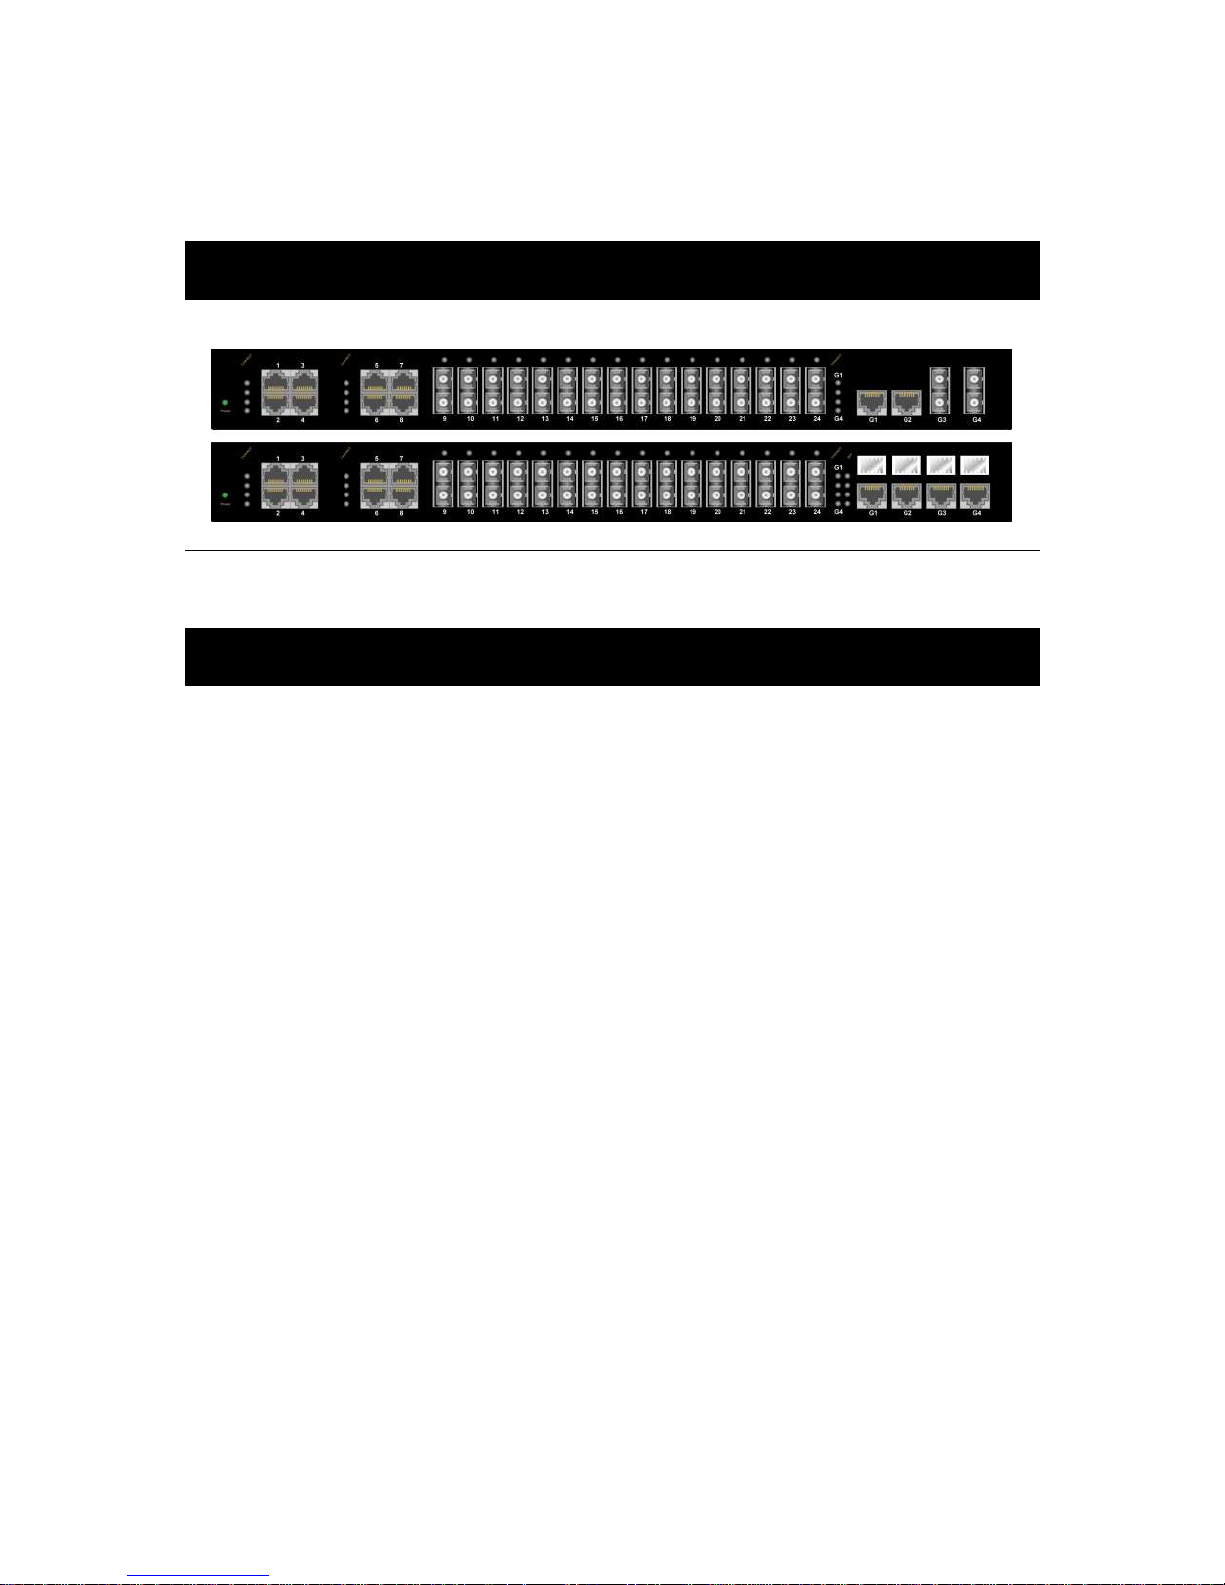
Industry Managed Ethernet Switch
Front View
Package Contents
When you unpack the product package, you shall find the items listed below. Please
inspect the contents, and report any apparent damage or missing items immediately to
your authorized reseller.
IES-2881
Quick Installation Guide
CD User Manual
RS-232 cable
Rackmount brackets with screws
Page 11
User Manual Page 11
Product Highlights
Basic Features
Meets NEMA TS1/TS2 Environmental requirements such as temperature, shock, and
vibration for traffic control equipment.
Meets EN61000-6-2 & EN61000-6-4 EMC Generic Standard Immunity for industrial
environment.
RS-232 console, Telnet, SNMP v1 & v2c & v3, RMON, Web Browser, and TFTP
management.
Supports Command Line Interface in RS-232 console.
Supports 8192 MAC addresses. Provides 3M bits memory buffer.
Supports IEEE802.3/802.3u/802.3ab/802.3z/802.3x. Auto-negotiation:
1000Mbps-full-duplex; 10/100Mbps-full/half-duplex; Auto MDI/MDIX.
100Base-FX: Multi mode SC or ST type, Single mode SC or ST type; 100Base-BX: WDM
Single mode SC type.
1000Base-SX/LX: Multi mode SC type, Single mode SC type; 1000Base-BX: WDM Single
mode SC type.
SFP socket for Gigabit fiber optic expansion.
Store-and-forward mechanism.
Full wire-speed forwarding rate.
AC inlet power socket: 100~240VAC, 50~60Hz internal universal PSU.
Terminal Block power input: +48VDC, -48VDC, 88~370VDC, or 90~264VAC.
Supports redundant power supplies for flexible application.
-40℃ to 75℃ (-40℉ to 167℉) operating temperature range.
Tested for functional operation @ -40℃ to 85℃ (-40℉ to 185℉).
Industry metal case.
Supports Rack Mounting installation.
Management Support
VLAN
Port-based VLAN
IEEE802.1Q tagged VLAN
TRUNKING
Port Trunking
PORT-SECURITY
Per-port programmable MAC address locking
Up to 24 Static Secure MAC addresses per port
IEEE802.1x Port-based Network Access Control
Page 12
User Manual Page 12
PORT-MIRRORING
Port-mirroring
QOS (IEEE802.1p Quality of Service)
4 priority queues
INTERNETWORKING PROTOCOLS
Bridging:
IEEE802.1s Multiple Spanning Tree
IEEE802.1w Rapid Spanning Tree
IEEE802.1D Spanning Tree compatible
IEEE802.1Q GVRP
Ring
IP Multicast:
IGMP Snooping
Rate Control
NTP
NETWORK MANAGEMENT METHODS
Console port access via RS-232 cable (CLI, Command Line Interface)
Telnet remote access
SNMP agent:
MIB-2 (RFC1213)
Bridge MIB (RFC1493)
RMON MIB (RFC2819) statistics, history, alarm and events
VLAN MIB (IEEE802.1Q/RFC2674)
Private MIB
Web browser
TFTP software-upgrade capability
Page 13
User Manual Page 13
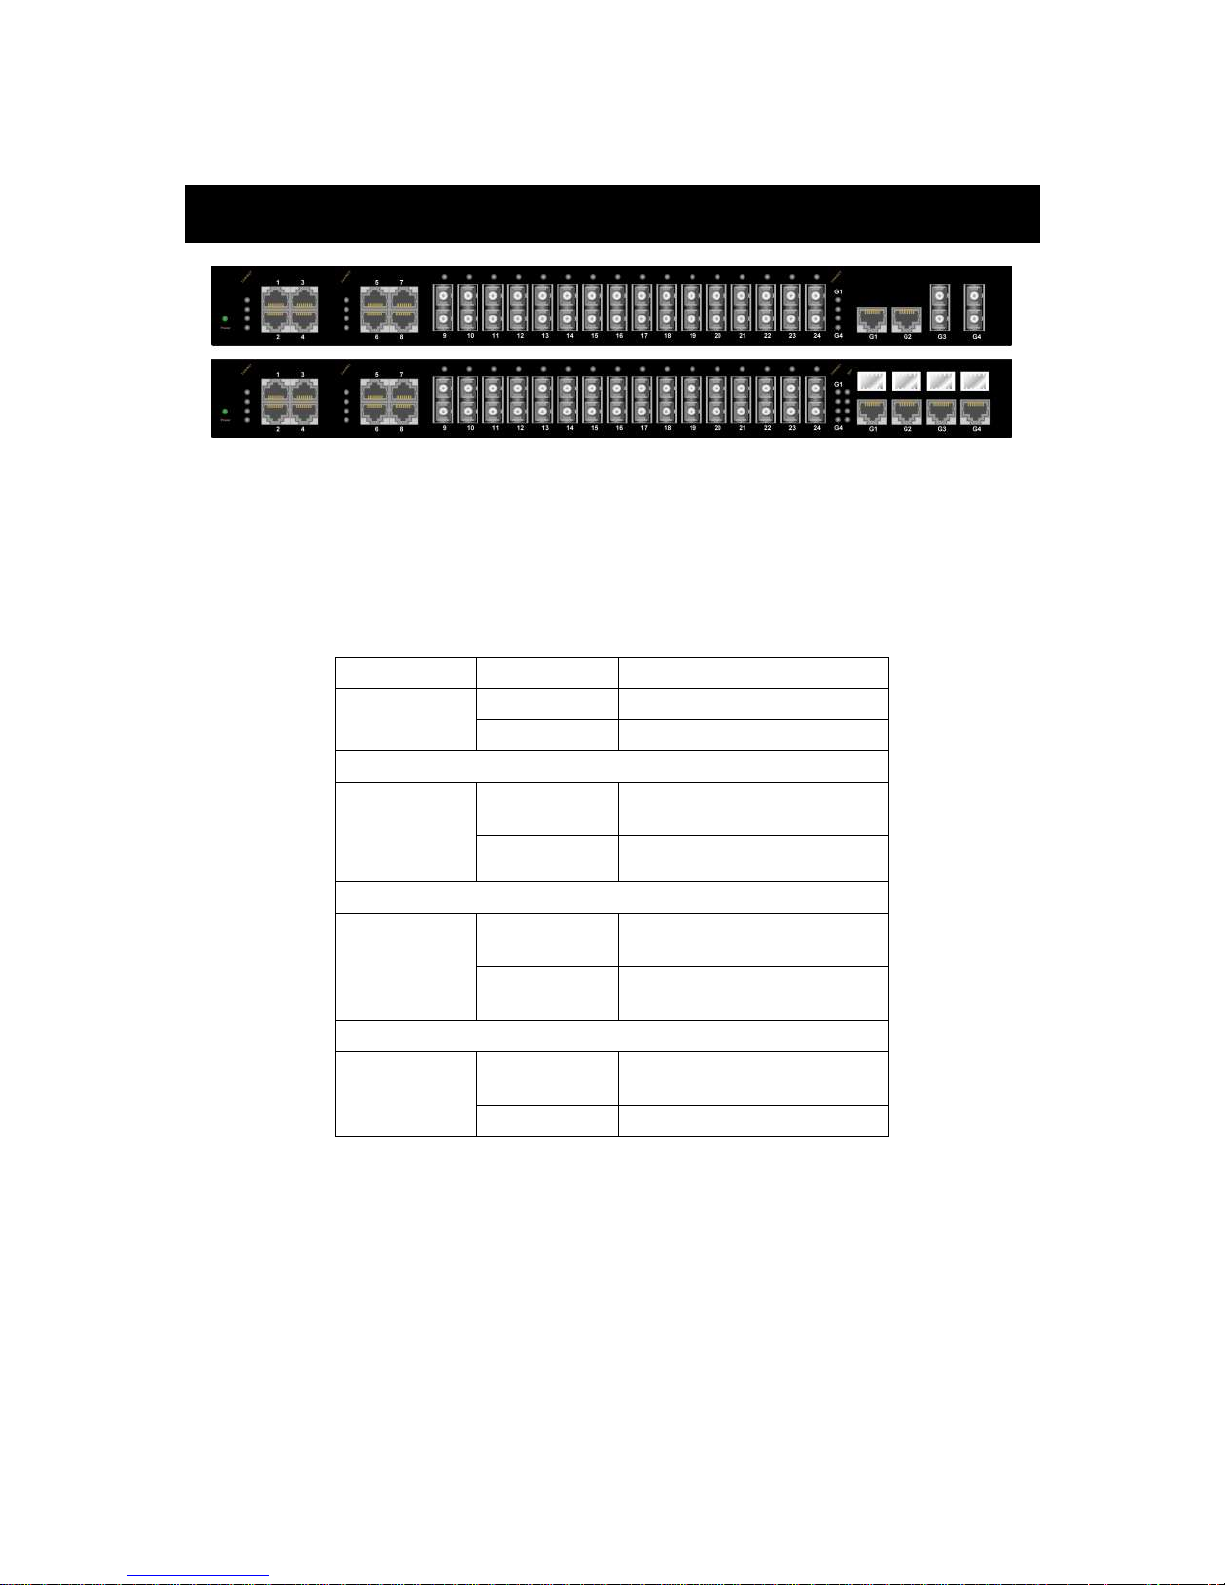
Front Panel Display
POWER
This LED comes on when the switch is properly connected to power and turned on.
Port Status LEDs
The LEDs are located on the front panel, displaying status for each respective port. Please
refer to the following table for more details.
LED
State
Indication
Power
Steady
Power on
Off
Power off
10/100Base-TX, 100Base-FX/BX
Link/ACT
Steady
A valid network connection
established
Flashing
Transmitting or receiving data
ACT stands for ACTIVITY
10/100/1000Base-TX, SFP, 1000Base-SX/LX/BX
Link/ACT
Steady
A valid network connection
established
Flashing
Transmitting or receiving data
ACT stands for ACTIVITY
SFP
SFP
Steady
A valid SFP connection
established
Off
Without SFP
Page 14
User Manual Page 14
Physical Ports
The Industry Managed Ethernet Switch provides:
24 FE + 4 GE Combo SFP Managed Switch -40 to 75C, IEC61850
CONNECTIVITY
RJ-45 connectors on TX ports
ST or SC connector on 100Base-FX fiber port
SC connector on 100Base-BX fiber port
SC connector on 1000Base-SX/LX/BX fiber port
Duplex LC connector on SFP 1000Base-SX/LX/BX fiber transceiver
MODE SELECTION
10Base-T full-duplex mode
10Base-T half-duplex mode
100Base-TX full-duplex mode
100Base-TX half-duplex mode
100Base-FX full-duplex mode
1000Base-T/SX/LX full-duplex mode
Auto-negotiating mode
Page 15
User Manual Page 15
Switch Management
Web-based browser interface
The switch also boasts a point-and-click browser-based interface that lets user access full
switch configuration and functionality from a Netscape or Internet Explorer browser.
Administration console via RS-232 serial port (CLI)
The switch provides an onboard serial port, which allows the switch to be configured via a
directly connected terminal.
External SNMP-based network management application
The switch can also be configured via SNMP.
Page 16
User Manual Page 16
Installation
This chapter gives step-by-step instructions about how to install the switch:
Selecting a Site for the Switch
As with any electric device, you should place the switch where it will not be subjected to
extreme temperatures, humidity, or electromagnetic interference. Specifically, the site you
select should meet the following requirements:
-The ambient temperature should be between -40°C to 75℃ (-40℉ to 167℉).
-The relative humidity should be less than 95 percent, non-condensing.
-Surrounding electrical devices should not exceed the electromagnetic field (RFC)
standards.
-Make sure that the switch receives adequate ventilation. Do not block the ventilation
holes on each side of the switch.
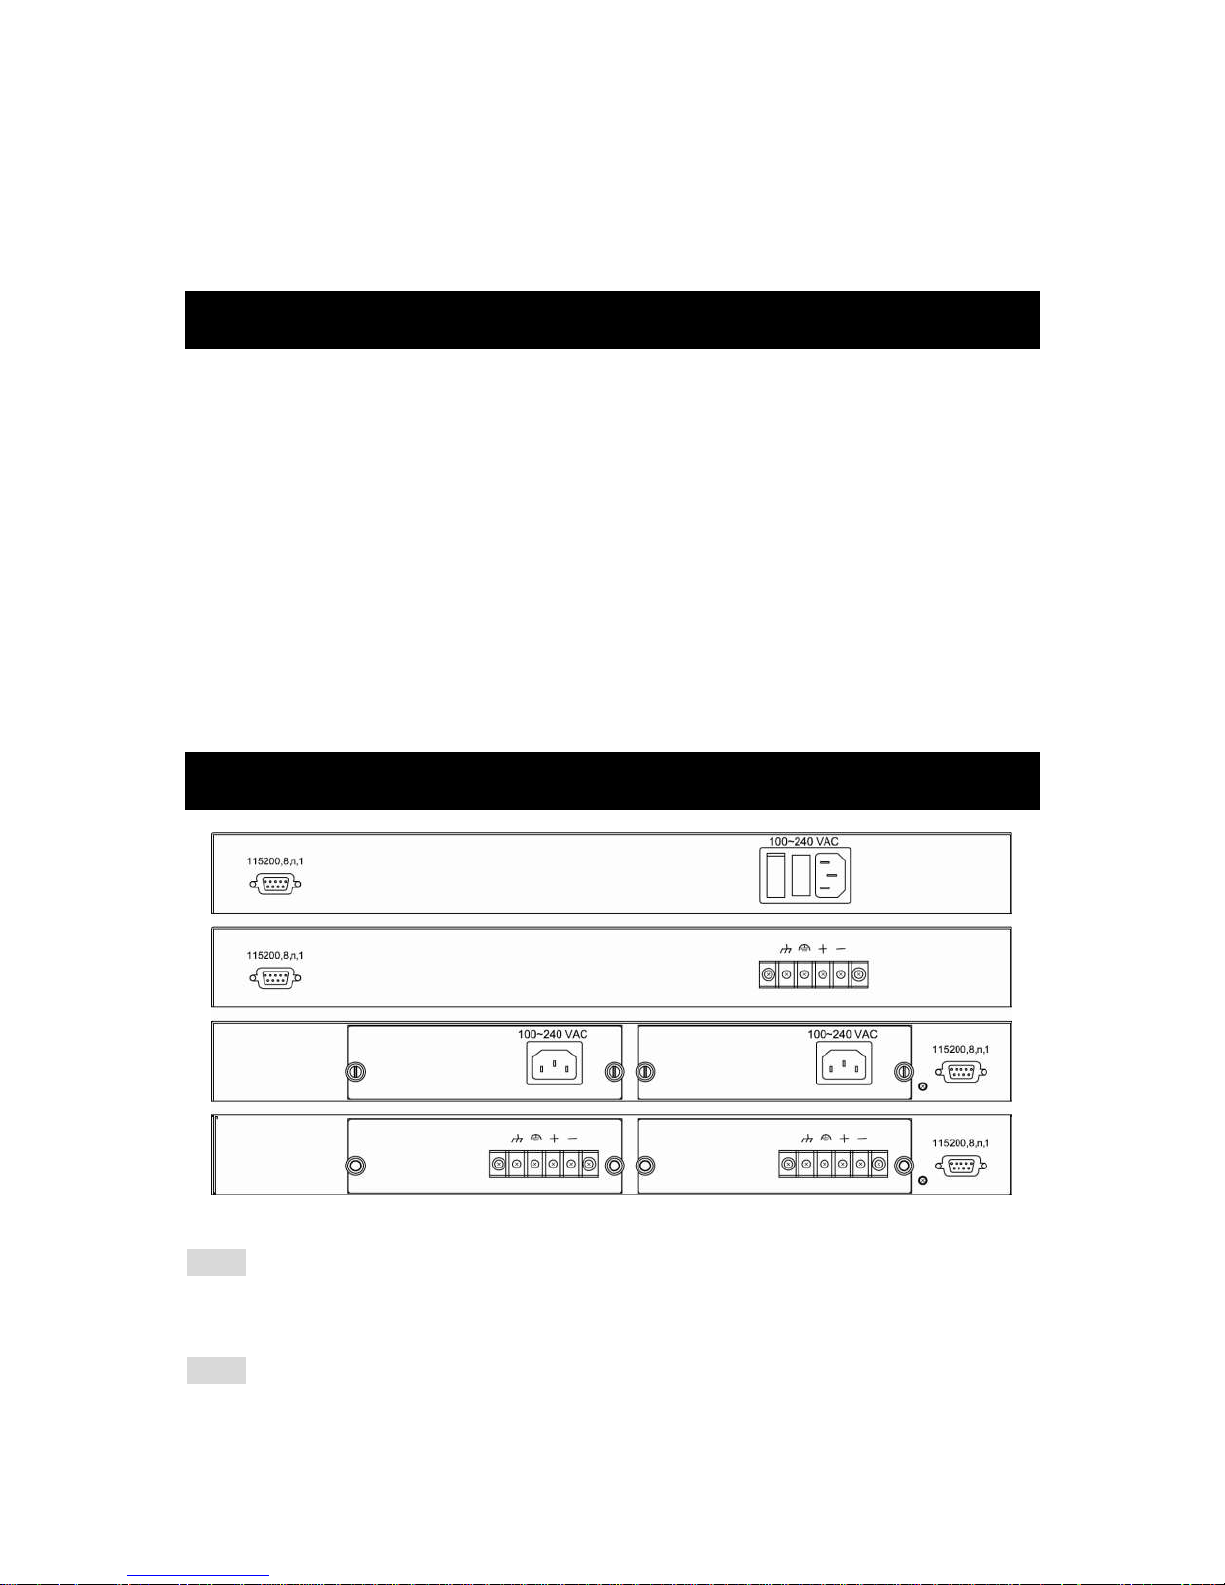
Connecting to Power
AC inlet power socket:
Step 1: Connect the supplied AC power cord to the receptacle on the back of the switch,
and then plug it into a standard AC outlet with a voltage range from 100 to 240 VAC. Turn
on the AC power switch at the back panel to turn on the switch.
Step 2: Turn off the AC switch if you want to shut down the switch.
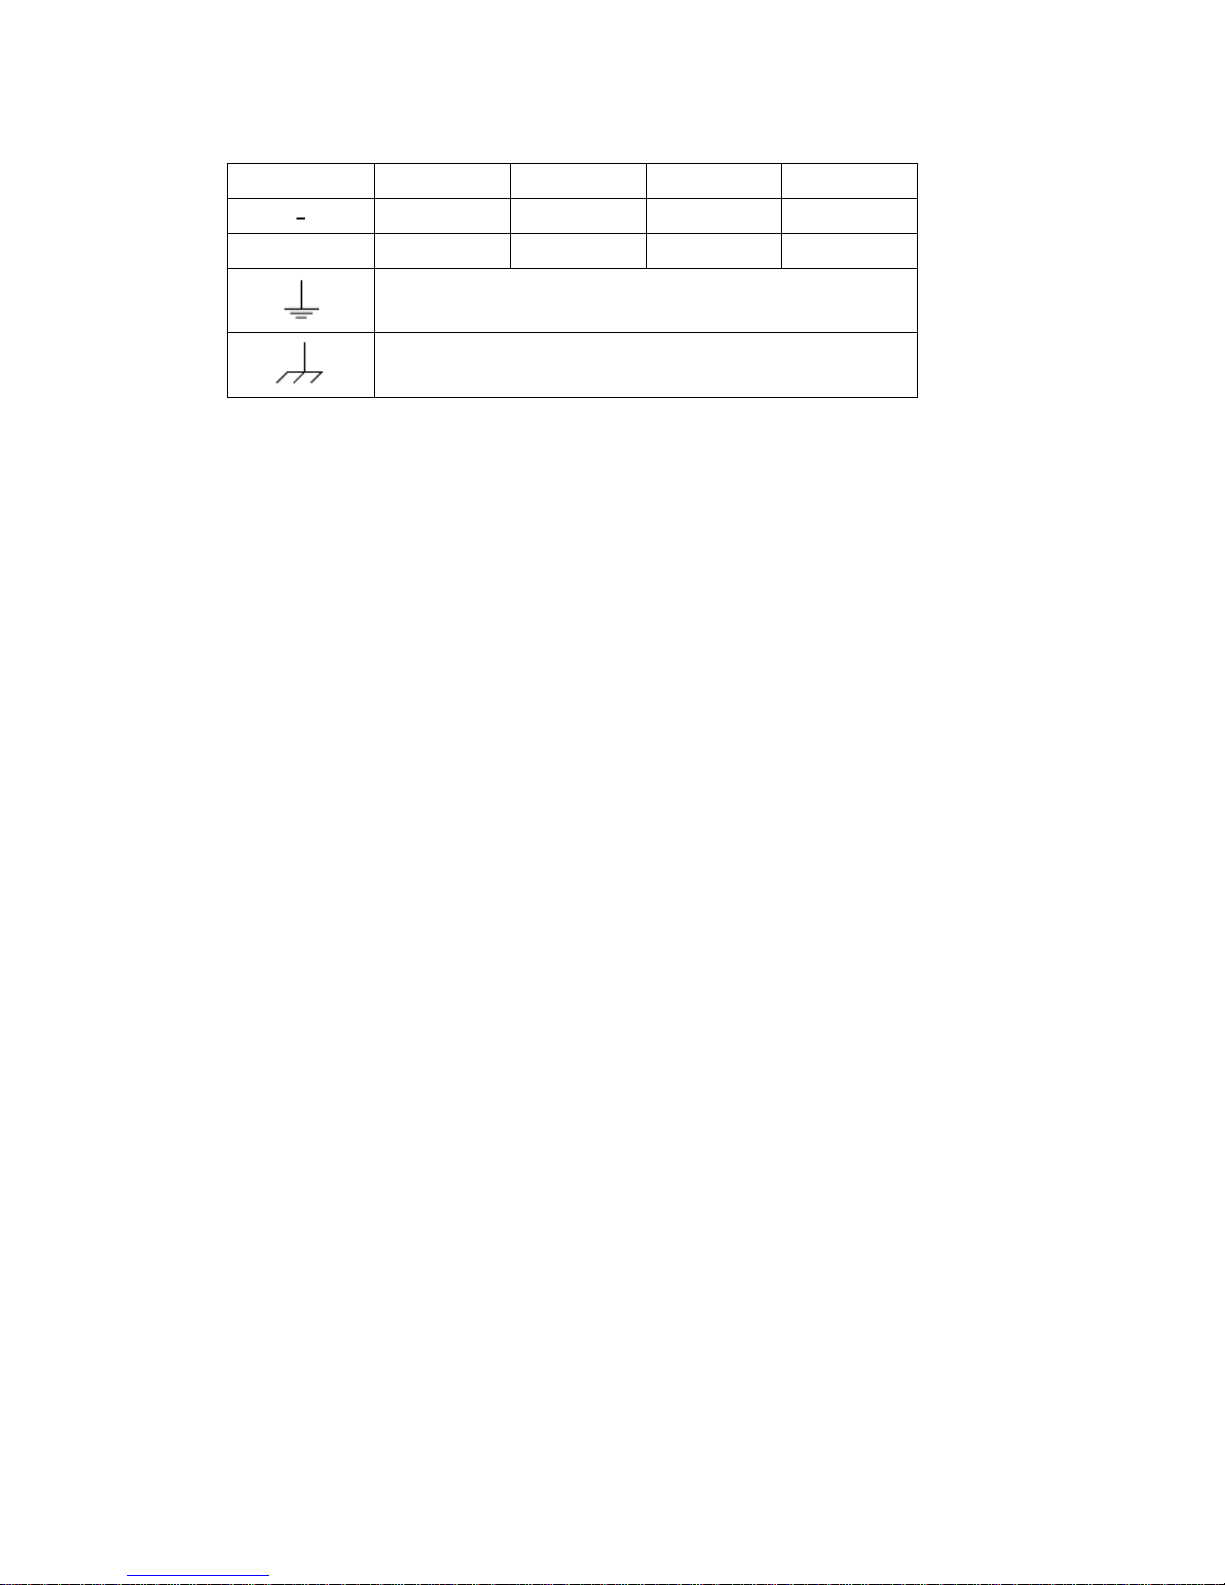
Terminal Block power input:
Page 17
User Manual Page 17
+48VDC
-48VDC
88-370VDC
90-264VAC
0
-48 0 N
+
+48
0
88-370
L
Earth Ground
Protect Ground
<Note> Dielectric withstand (Hipot) test for DC power input, must remove metal chip
between Earth Ground and Protect Ground of the terminal block power input to avoid
damage to the Switch.
Procedures to Replace Inactive Redundant Power Supply
Module
These procedures provide instructions on removing inactive redundant power supply
module and installing a new redundant power supply module in Managed Ethernet
Switch while Managed Ethernet Switch still keeps operating normally with another
redundant power supply module.
1. Make sure to turn off the power source connected to inactive redundant power
supply module first, by loosening terminal block screws and disconnect power cables
from terminal block on inactive redundant power supply module.
2. Loosen inactive redundant power supply module screws and remove inactive
redundant power supply module from redundant power supply slot of Managed
Ethernet Switch.
3. Slide in new redundant power supply module in redundant power supply slot of
Managed Ethernet Switch and tighten new redundant power supply module screws.
4. Connect power cables to terminal block on new redundant power supply module by
tightening terminal block screws.
5. Turn on the power source connected to new redundant power supply module.
Page 18
User Manual Page 18
Connecting to Your Network
Cable Type & Length
It is necessary to follow the cable specifications below when connecting the switch to your
network. Use appropriate cables that meet your speed and cabling requirements.
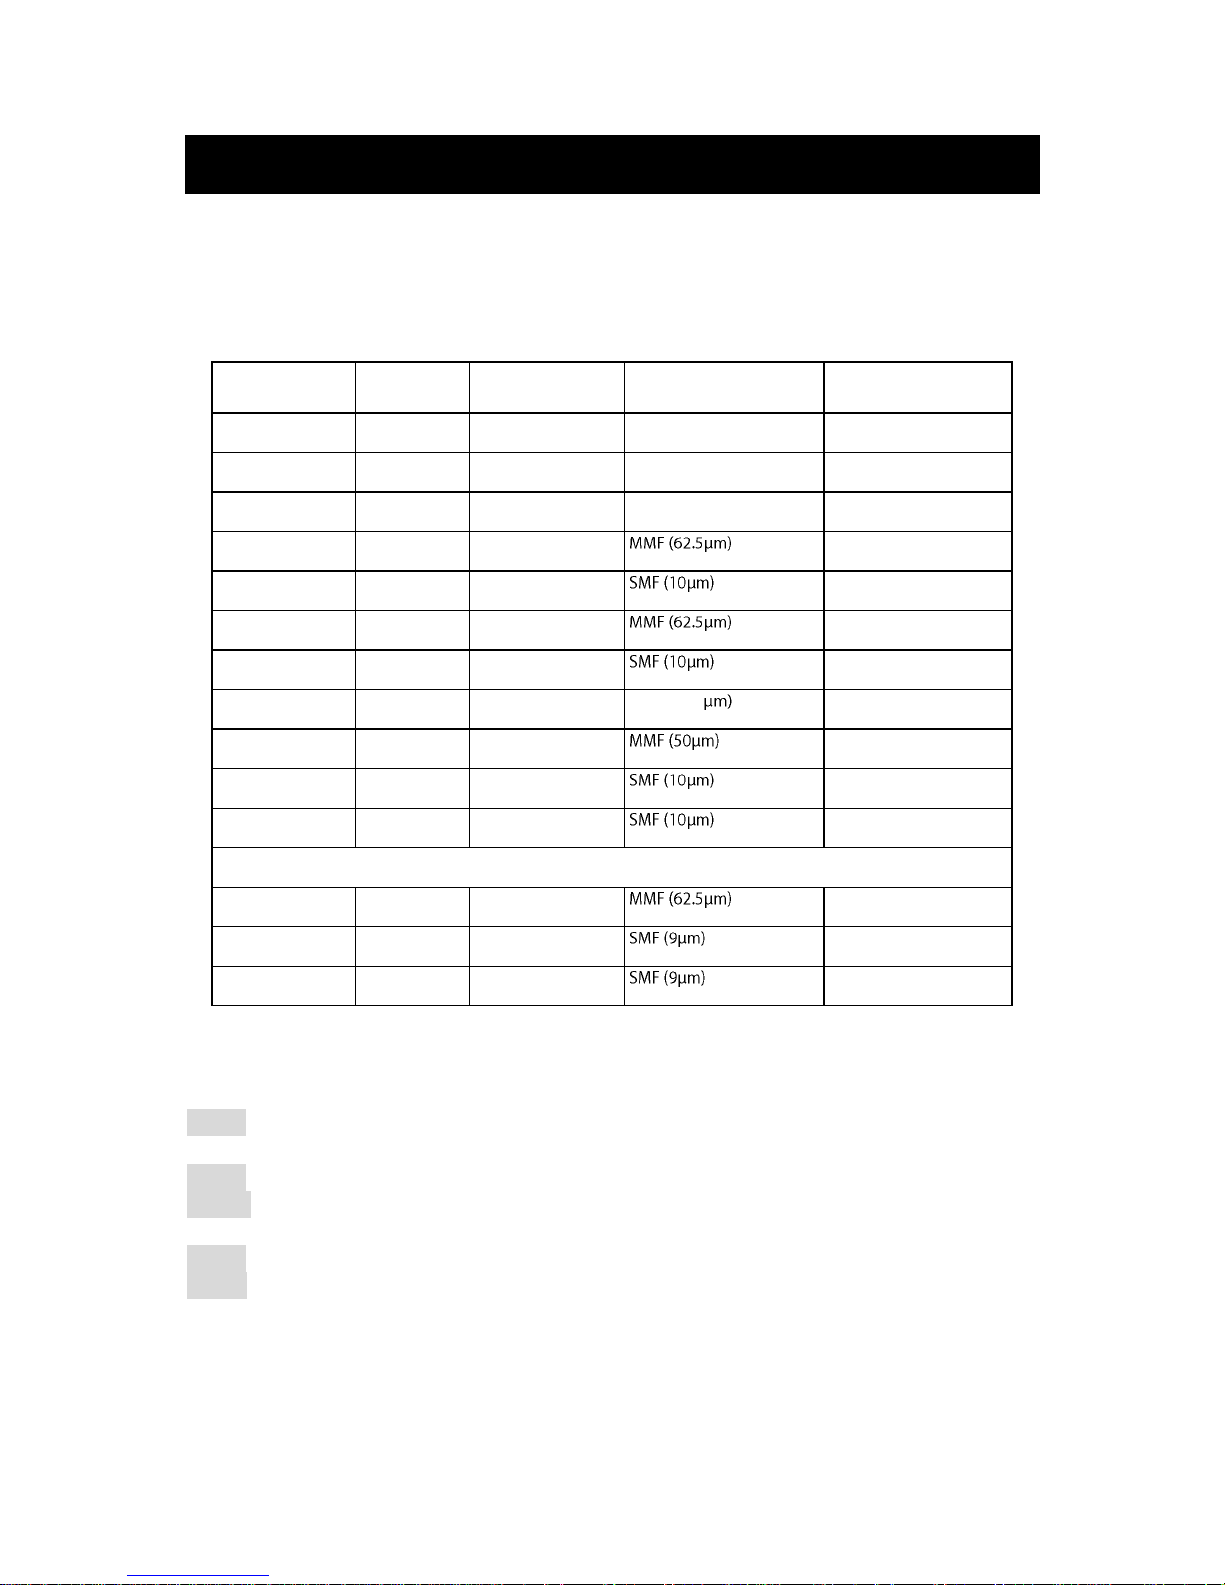
Cable Specifications
Speed
Connector
Port Speed
Half/Full Duplex
Cable
Max. Distance
10Base-T
RJ-45
10/20 Mbps
2-pair UTP/STP Cat. 3, 4, 5
100 m
100Base-TX
RJ-45
100/200 Mbps
2-pair UTP/STP Cat. 5
100 m
1000Base-T
RJ-45
2000 Mbps
4-pair UTP/STP Cat. 5
100 m
100Base-FX
ST, SC
200 Mbps
2 km
100Base-FX
ST, SC
200 Mbps
20, 40, 75, 100 km
100Base-BX
SC
200 Mbps
2, 5 km
100Base-BX
SC
200 Mbps
20, 40 km
1000Base-SX
SC
2000 Mbps
MMF (62.5
220 m, 2 km
1000Base-SX
SC
2000 Mbps
550 m
1000Base-LX
SC
2000 Mbps
10, 20, 50 km
1000Base-BX
SC
2000 Mbps
20, 40 km
SFP
1000Base-SX
Duplex LC
2000 Mbps
550 m, 2 km
1000Base-LX
Duplex LC
2000 Mbps
10, 40, 60 km
1000Base-BX
Duplex LC
2000 Mbps
70 km
Cabling
Step 1: First, ensure the power of the switch and end devices are turned off.
<Note> Always ensure that the power is off before any installation.
Step 2: Prepare cable with corresponding connectors for each type of port in use.
Step 3: Consult Cable Specifications Table on previous page for cabling requirements
based on connectors and speed.
Step 4: Connect one end of the cable to the switch and the other end to a desired device.
Step 5: Once the connections between two end devices are made successfully, turn on the
power and the switch is operational.
Note: IES-2881 packs with 24 100Base SFP slots + 4 Gigabit Combo SFP slots. Contact us for
more options in details
Page 19
User Manual Page 19
Switch Management
This chapter explains the methods that you can use to configure management access to
the switch. It describes the types of management applications and the communication
and management protocols that deliver data between your management device
(workstation or personal computer) and the system. It also contains information about
port connection options.
This chapter covers the following topics:
Management Access Overview
Key Concepts
Key Guidelines for Implementation
Web Management Access
Administration Console Access
SNMP Access
Standards, Protocols, and Related Reading
Management Access Overview
The switch gives you the flexibility to access and manage the switch using any or all of the
following methods.
The web browser interface and administration console (CLI) support are embedded in the
switch software and are available for immediate use.
Page 20
User Manual Page 20
Administration Console (CLI)
The administration console is an internal, character-oriented, Command Line Interface (CLI)
for performing system administration such as displaying statistics or changing option
settings. Using this method, you can view the administration console from a terminal,
port. There are two ways to use this management method: direct access or modem access.
The following sections describe these methods.
Direct Access
Direct access to the administration console is achieved by directly connecting a terminal
or a PC equipped with a terminal-emulation program (such as HyperTerminal) to the
switch console port.
When using the management method, configure the terminal-emulation program to use
the following parameters (you can change these settings after login):
[DEFAULT PARAMETERS]
115,200bps
8 data bits
No parity
1 stop bit
This management method is often preferred because you can remain connected and
monitor the system during system reboots. Also, certain error messages are sent to the
serial port, regardless of the interface through which the associated action was initiated. A
Macintosh or PC attachment can use any terminal-emulation program for connecting to
the terminal serial port. A workstation attachment under UNIX can use an emulator such
as TIP.
Modem Access
external modem attached to the console port. The switch management program provides
Console Port screen, accessible from the Basic Management screen that lets you
configure parameters for modem access.
When you have configured the external modem from the administration console, the
switch transmits characters that you have entered as output on the modem port. The
switch echoes characters that it receives as input on the modem port to the current
administration console session. The console appears to be directly connected to the
external modem.
Page 21
User Manual Page 21
Web Management
The switch provides a browser interface that lets you configure and manage the switch
remotely.
applications directly in your web browser by entering the IP address of the switch. You can
then use your web browser to list and manage switch configuration parameters from one
SNMP-Based Network Management
You can use an external SNMP-based application to configure and manage the switch. This
management method requires the SNMP agent on the switch and the SNMP Network
Management Station to use the same community string. This management method, in fact,
uses two community strings: the get community string and the set community string. If
the SNMP Network management station only knows the set community string, it can read
and write to the MIBs. However, if it only knows the get community string, it can only read
MIBs. The default get and set community strings for the switch are public.
Protocols
The switch supports the following protocols:
VIRTUAL TERMINAL PROTOCOLS, SUCH AS TELNET
A virtual terminal protocol is a software program, such as Telnet, that allows you to
establish a management session from a Macintosh, a PC, or a UNIX workstation. Because
Telnet runs over TCP/IP, you must have at least one IP address configured on the switch
before you can establish access to it with a virtual terminal protocol.
<Note> Terminal emulation is different from a virtual terminal protocol in that you must
connect a terminal directly to the console port.
SIMPLE NETWORK MANAGEMENT PROTOCOL (SNMP)
SNMP is the standard management protocol for multivendor IP networks. SNMP supports
transaction-based queries that allow the protocol to format messages and to transmit
information between reporting devices and data-collection programs. SNMP runs on top
of the User Datagram Protocol (UDP), offering a connectionless-mode service.
Page 22
User Manual Page 22
Management Architecture
All of the management application modules use the same Messaging Application
Programming Interface (MAPI). By unifying management methods with a single MAPI,
configuration parameters set using one method (e.g. console port) are immediately
displayed the other management methods (e.g. SNMP agent of web browser).
The management architecture of the switch adheres to the IEEE open standard. This
compliance assures customers that the switch is compatible with, and will interoperate
with other solutions that adhere to the same open standard.
Page 23
User Manual Page 23
Web-Based Browser Management
The switch provides a web-based browser interface for configuring and managing the
switch. This interface allows you to access the switch using a preferred web browser.
This chapter describes how to configure the switch using its web-based browser interface.
Page 24
User Manual Page 24
SNMP & RMON Management
Remote Monitoring (RMON) capabilities.
Overview
RMON is an abbreviation for the Remote Monitoring MIB (Management Information Base).
RMON is a system defined by the Internet Engineering Task Force (IETF) document RFC
2819, which defines how networks can be monitored remotely.
RMONs typically consist of two components: an RMON probe and a management
workstation:
- The RMON probe is an intelligent device or software agent that continually collects
statistics about a LAN segment or VLAN. The RMON probe transfers the collected data to
a management workstation on request or when a pre-defined threshold is reached.
- The management workstation collects the statistics that the RMON probe gathers. The
workstation can reside on the same network as the probe, or it can have an in-band or
out-of-band connection to the probe.
The switch provides RMON capabilities that allow network administrators to set
parameters and view statistical counters defined in MIB-II, Bridge MIB, and RMON MIB.
RMON activities are performed at a Network Management Station running an SNMP
network management application with graphical user interface.
SNMP Agent and MIB-2 (RFC 1213)
The SNMP Agent running on the switch manager CPU is responsible for:
- Retrieving MIB counters from various layers of software modules according to the SNMP
GET/GET NEXT frame messages.
- Setting MIB variables according to the SNMP SET frame message.
- Generating an SNMP TRAP frame message to the Network Management Station if the
threshold of a certain MIB counter is reached or if other trap conditions (such as the
following) are met:
Page 25
User Manual Page 25
WARM START
COLD START
LINK UP
LINK DOWN
AUTHENTICATION FAILURE
RISING ALARM
FALLING ALARM
TOPOLOGY ALARM
MIB-II defines a set of manageable objects in various layers of the TCP/IP protocol suites.
MIB-II covers all manageable objects from layer 1 to layer 4, and, as a result, is the major
SNMP MIB supported by all vendors in the networking industry. The switch supports a
complete implementation of SNMP Agent and MIB-II.
RMON MIB (RFC 2819) & Bridge MIB (RFC 1493)
The switch provides hardware-based RMON counters in the switch chipset. The switch
manager CPU polls these counters periodically to collect the statistics in a format that
complies with the RMON MIB definition.
RMON Groups Supported
The switch supports the following RMON MIB groups defined in RFC 2819:
- RMON Statistics Group maintains utilization and error statistics for the switch port
being monitored.
- RMON History Group gathers and stores periodic statistical samples from the previous
Statistics Group.
- RMON Alarm Group allows a network administrator to define alarm thresholds for any
MIB variable. An alarm can be associated with Low Threshold, High Threshold, or both. A
trigger can trigger an alarm when the value of a specific MIB variable exceeds a threshold,
falls below a threshold, or exceeds or falls below a threshold.
- RMON Event Group allows a network administrator to define actions based on alarms.
SNMP Traps are generated when RMON Alarms are triggered. The action taken in the
Network Management Station depends on the specific network management application.
Bridge Groups Supported
The switch supports the following four groups of Bridge MIB (RFC 1493):
Page 26
User Manual Page 26
- The dot1dBase Group a mandatory group that contains the objects applicable to all
types of bridges.
- The dot1dStp Group
Spanning Tree Protocol. If a node does not implement the Spanning Tree Protocol, this
group will not be implemented. This group is applicable to any transparent only, source
route, or SRT bridge that implements the Spanning Tree Protocol.
- The dot1dTp Group contains objects that des
status. This group is applicable to transparent operation only and SRT bridges.
- The dot1dStatic Group -address
filtering status. This group is applicable to any type of bridge which performs
destination-address filtering.
Page 27
User Manual Page 27
Web-Based Browser Management
The switch provides a web-based browser interface for configuring and managing the
switch. This interface allows you to access the switch using a preferred web browser.
This chapter describes how to configure the switch using its web-based browser interface.
Logging on to the switch
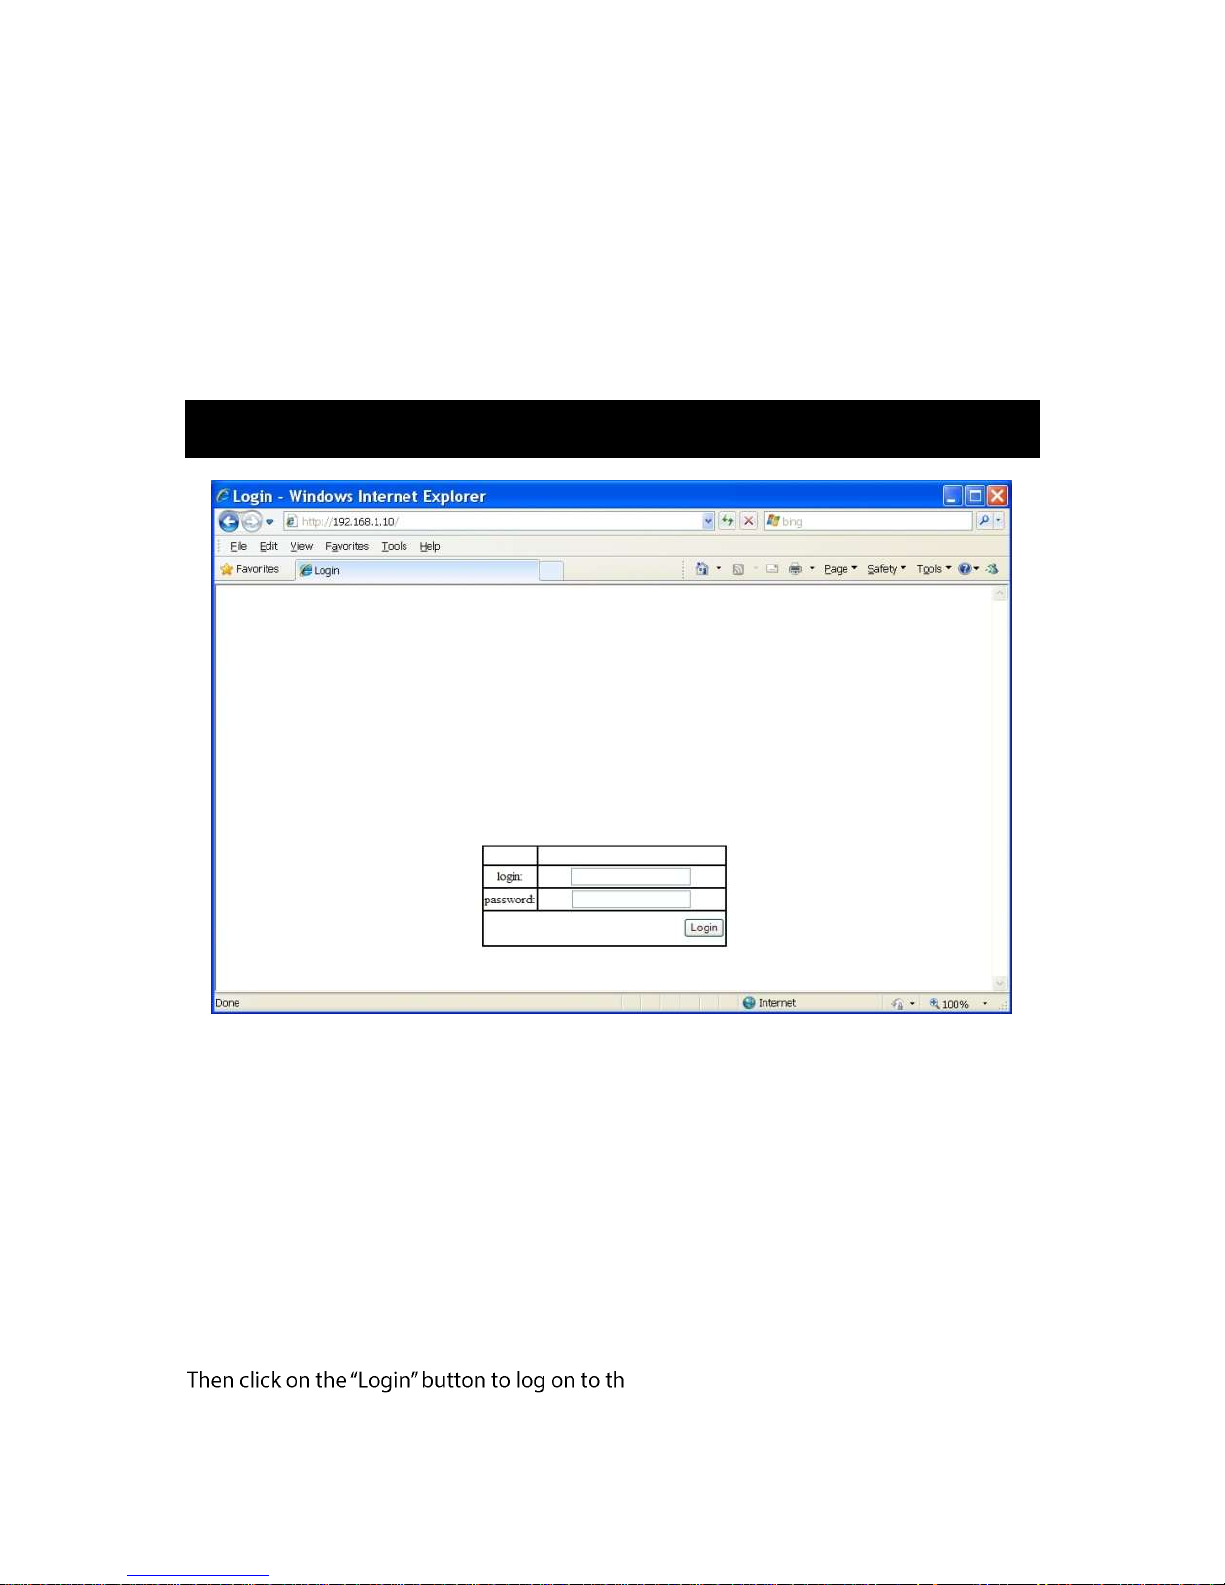
SWITCH IP ADDRESS
In your web browser, specify the IP address of the switch. Default IP address is
192.168.1.10.
LOGIN
Enter the factory default login ID: root.
PASSWORD
Enter the factory default password (no password). Or enter a user-defined password if you
followed the instructions later and changed the factory default password.
e switch.
Page 28
User Manual Page 28
Understanding the Browser Interface
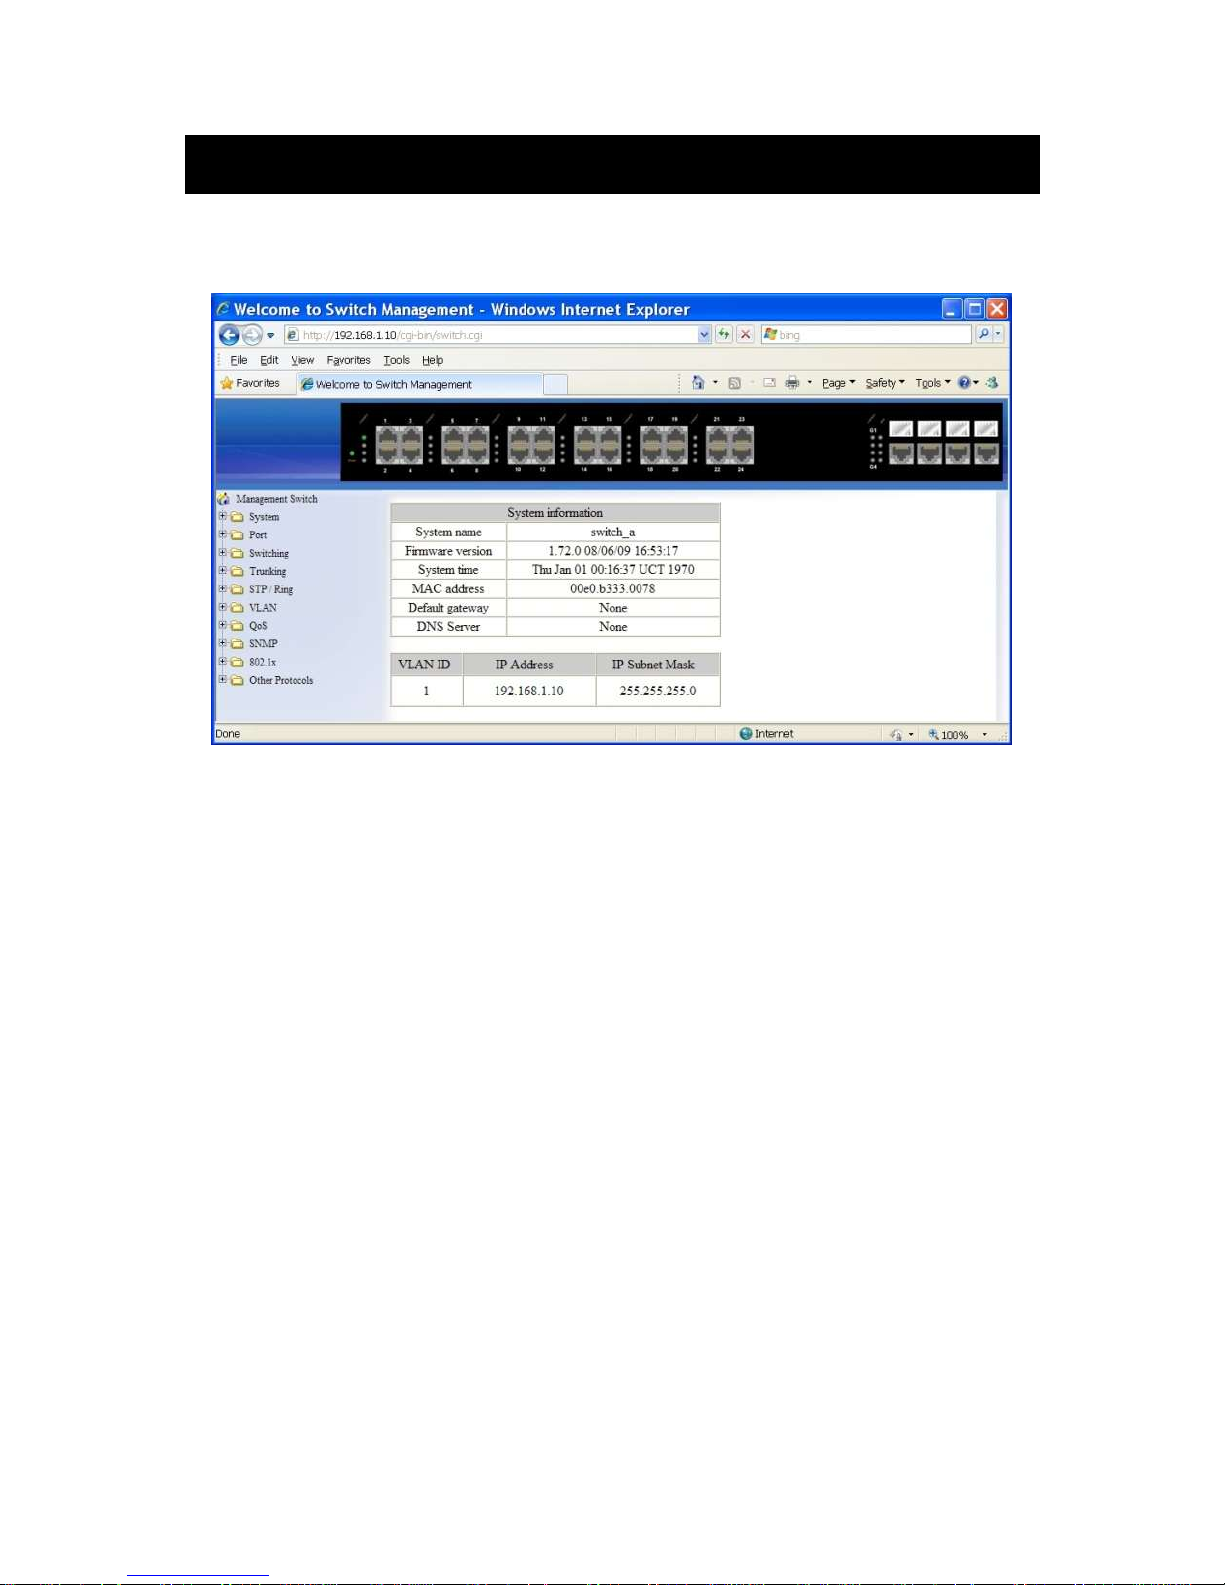
The web browser interface provides groups of point-and-click buttons at the left field of
the screen for configuring and managing the switch.
SYSTEM
System Information, System Name/Password, IP Address, Save Configuration, Firmware
Upgrade, Reboot, Logout
PORT
Configuration, Port Status, Rate Control, RMON Statistics, Per Port Vlan Activities
SWITCHING
Bridging, Static MAC Entry, Port Mirroring
TRUNKING
Port Trunking
STP / RING
Global Configuration, RSTP Port Setting, MSTP Properties, MSTP Instance Setting, MSTP
Port Setting, Ring Setting
VLAN
VLAN Mode Setting, 802.1Q VLAN Setting, 802.1Q Port Setting, Port Based VLAN
Page 29
User Manual Page 29
QOS
Global Configuration, 802.1p Priority, DSCP
SNMP
SNMP General Setting, SNMP v1/v2c, SNMP v3
802.1X
Radius Configuration, Port Authentication
OTHER PROTOCOLS
GVRP, IGMP Snooping, NTP
Page 30
User Manual Page 30
System
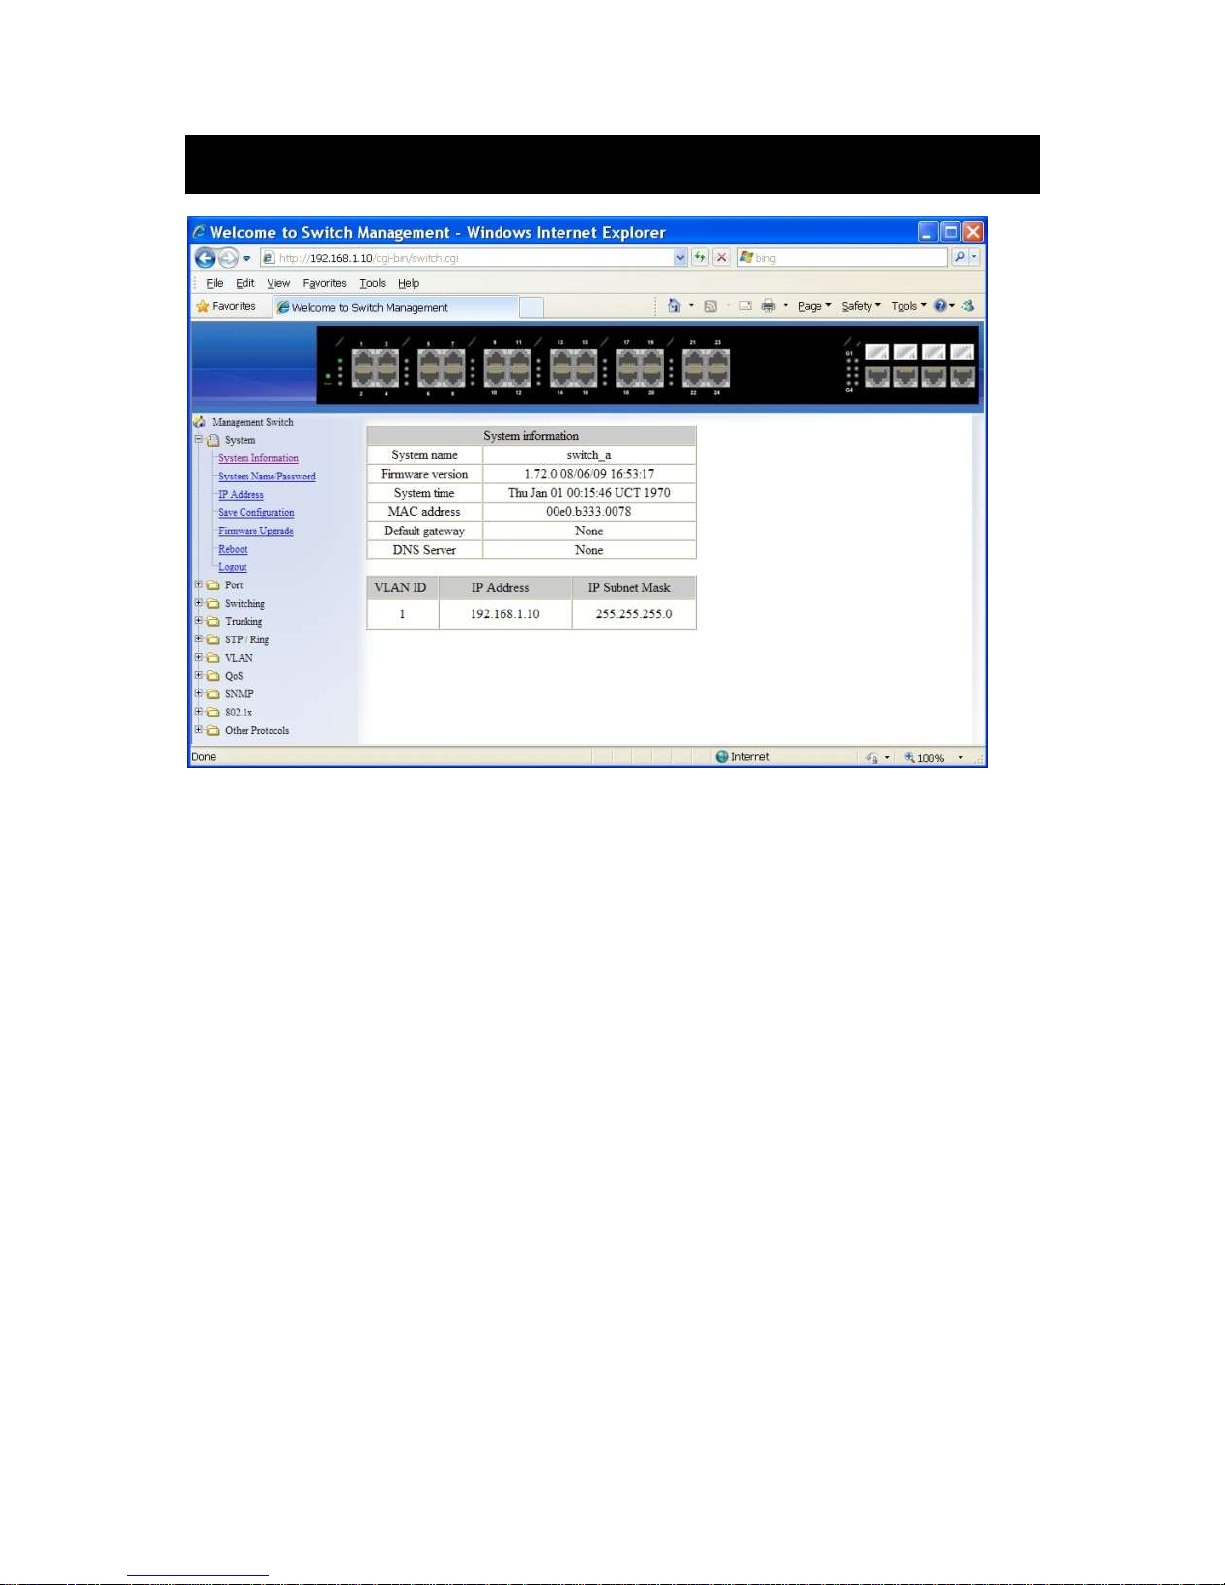
System Information
The System name, Firmware version, MAC address, Default gateway, VLAN ID, IP Address,
and IP Subnet Mask of Switch.
Page 31
User Manual Page 31
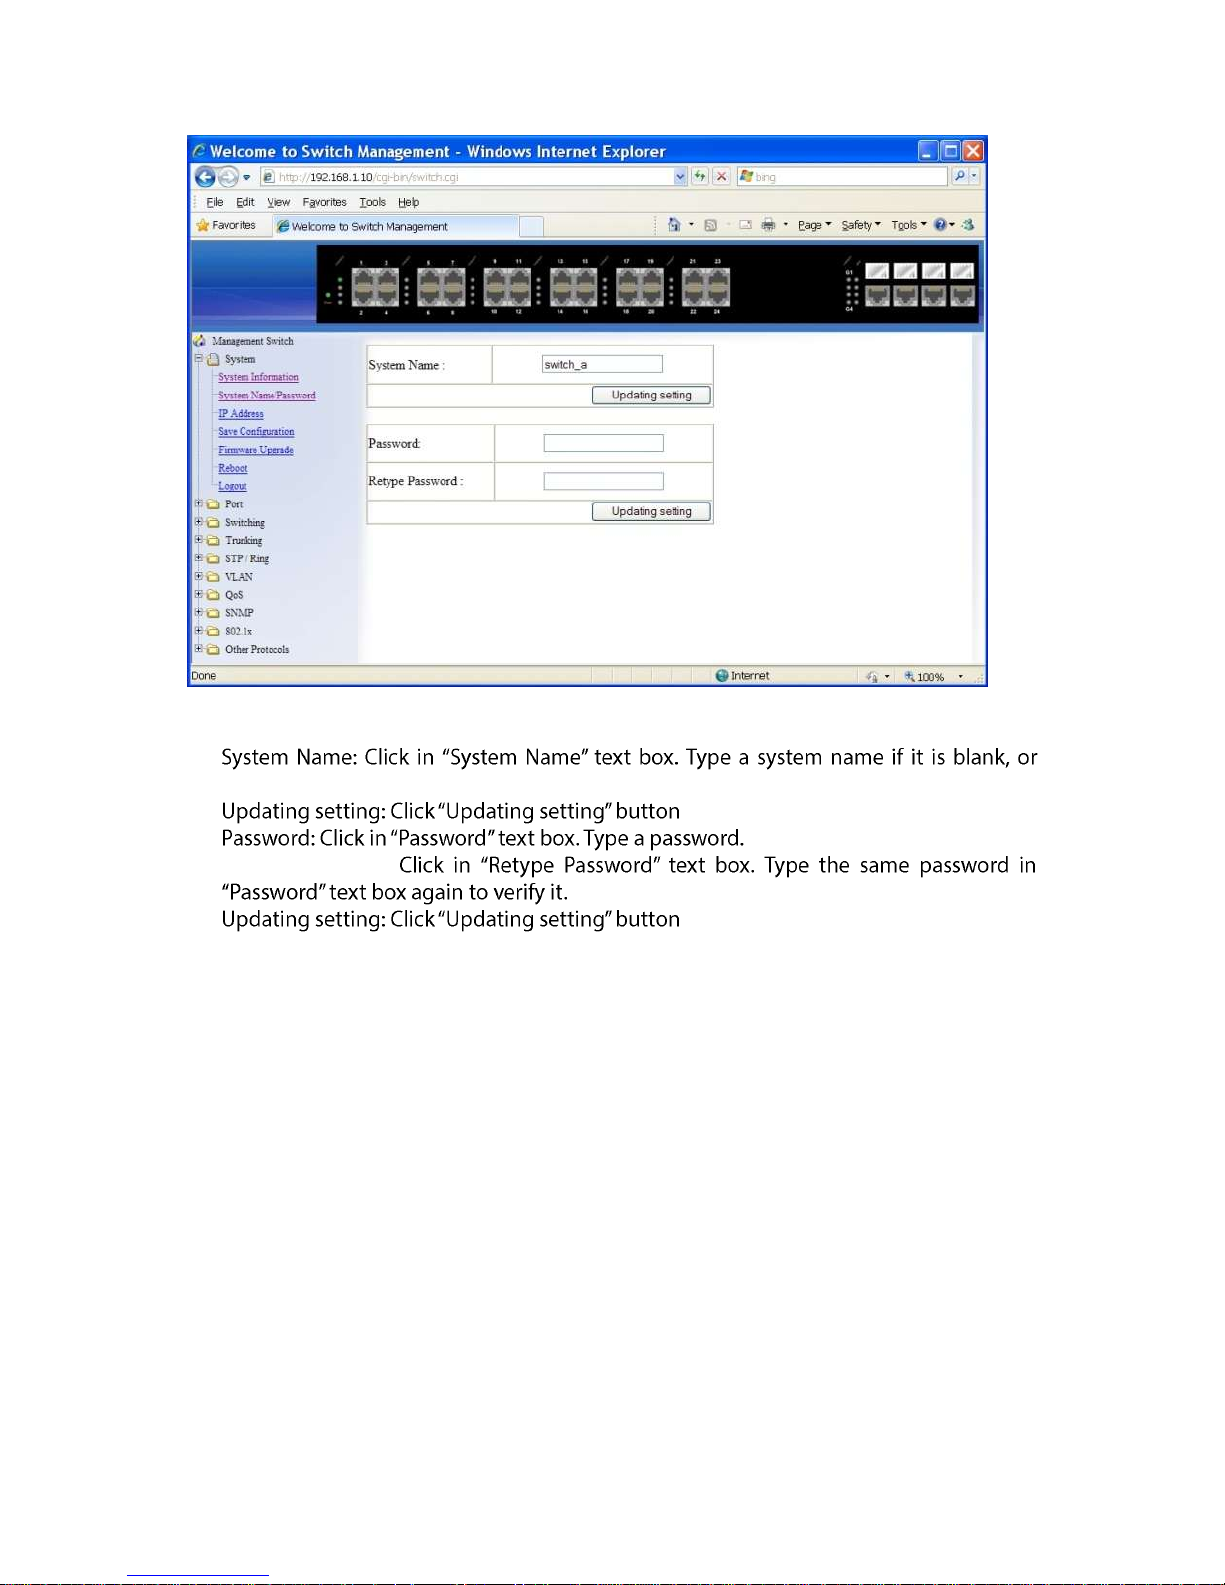
System Name/Password
1.
replace the current system name with a new one.
2. to update your settings.
3.
4. Retype Password:
5. to update your settings.
Page 32
User Manual Page 32
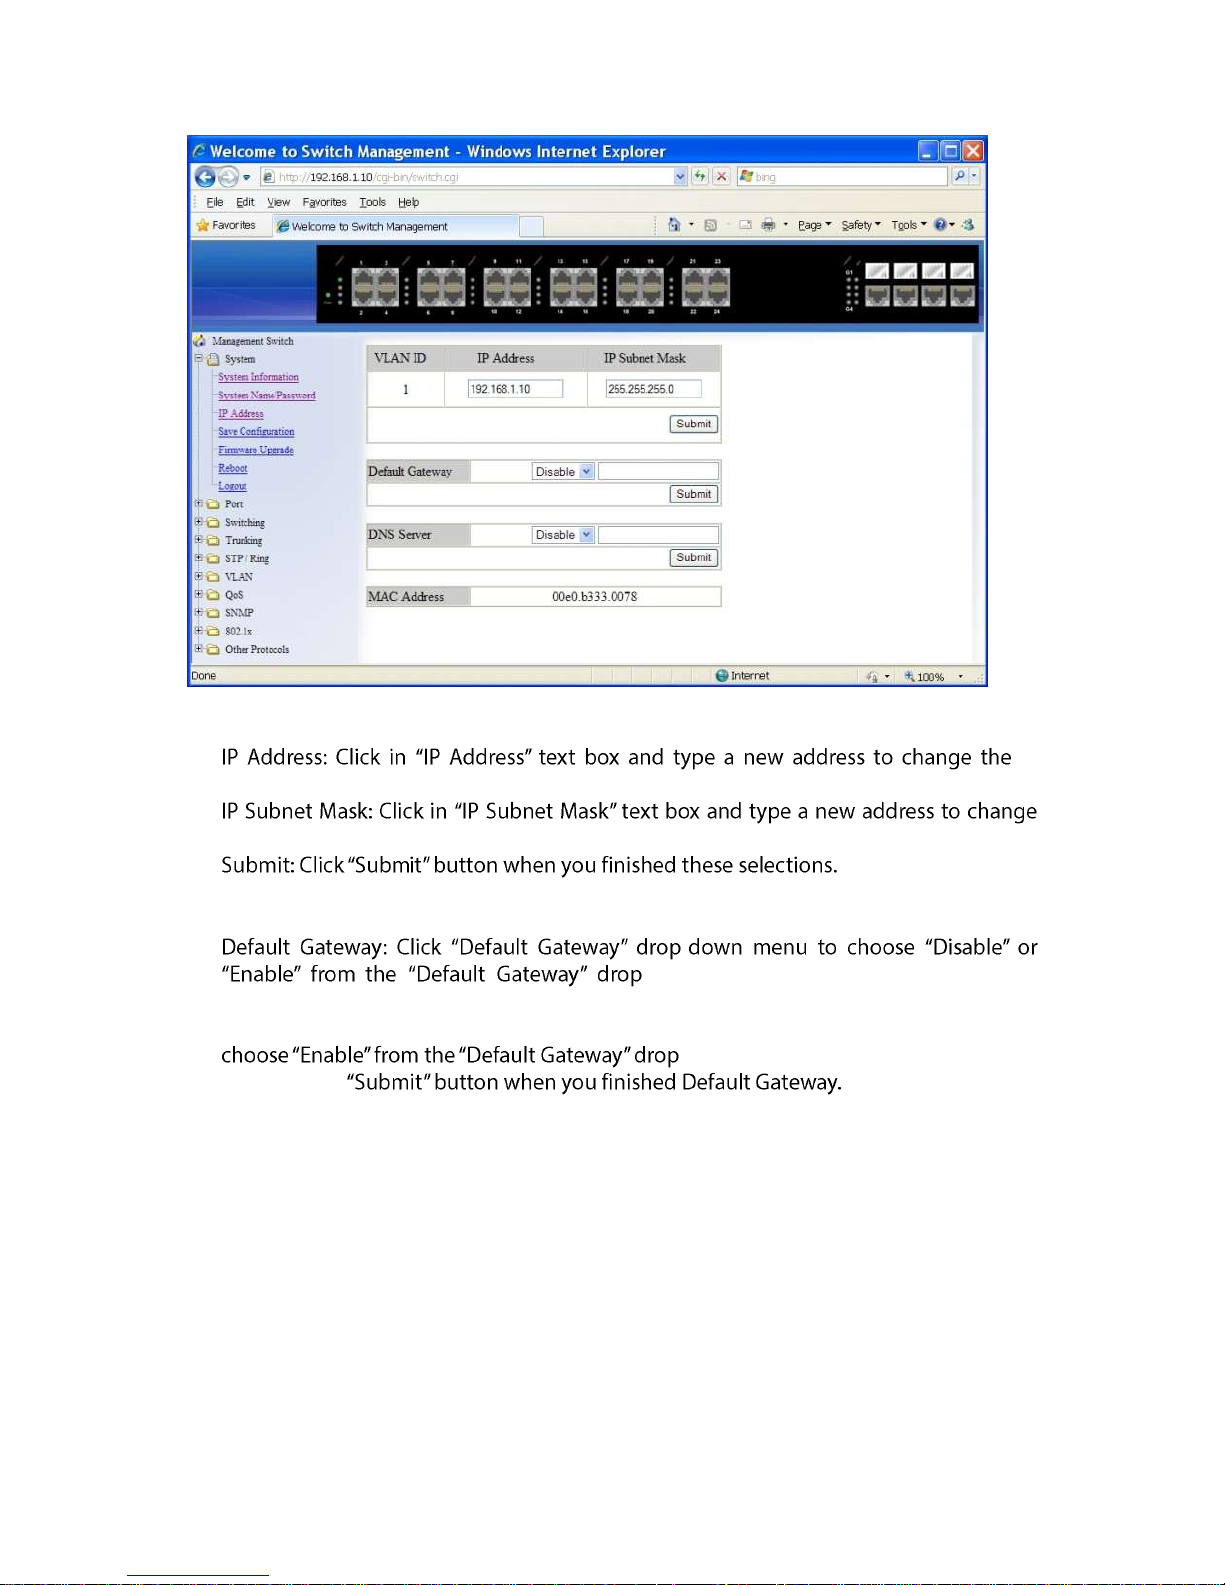
IP Address
1. IP
Address.
2.
the IP Subnet Mask.
3.
4. You need to enter the new IP address on the browser and reconnect to the switch after
IP or subnet mask are changed.
5. -
-down list to disable or enable Default
Gateway Setting for the switch.
Click the text box and type a new address to change the Default Gateway. (Need to
-down menu.)
6. Submit: Click
Page 33
User Manual Page 33
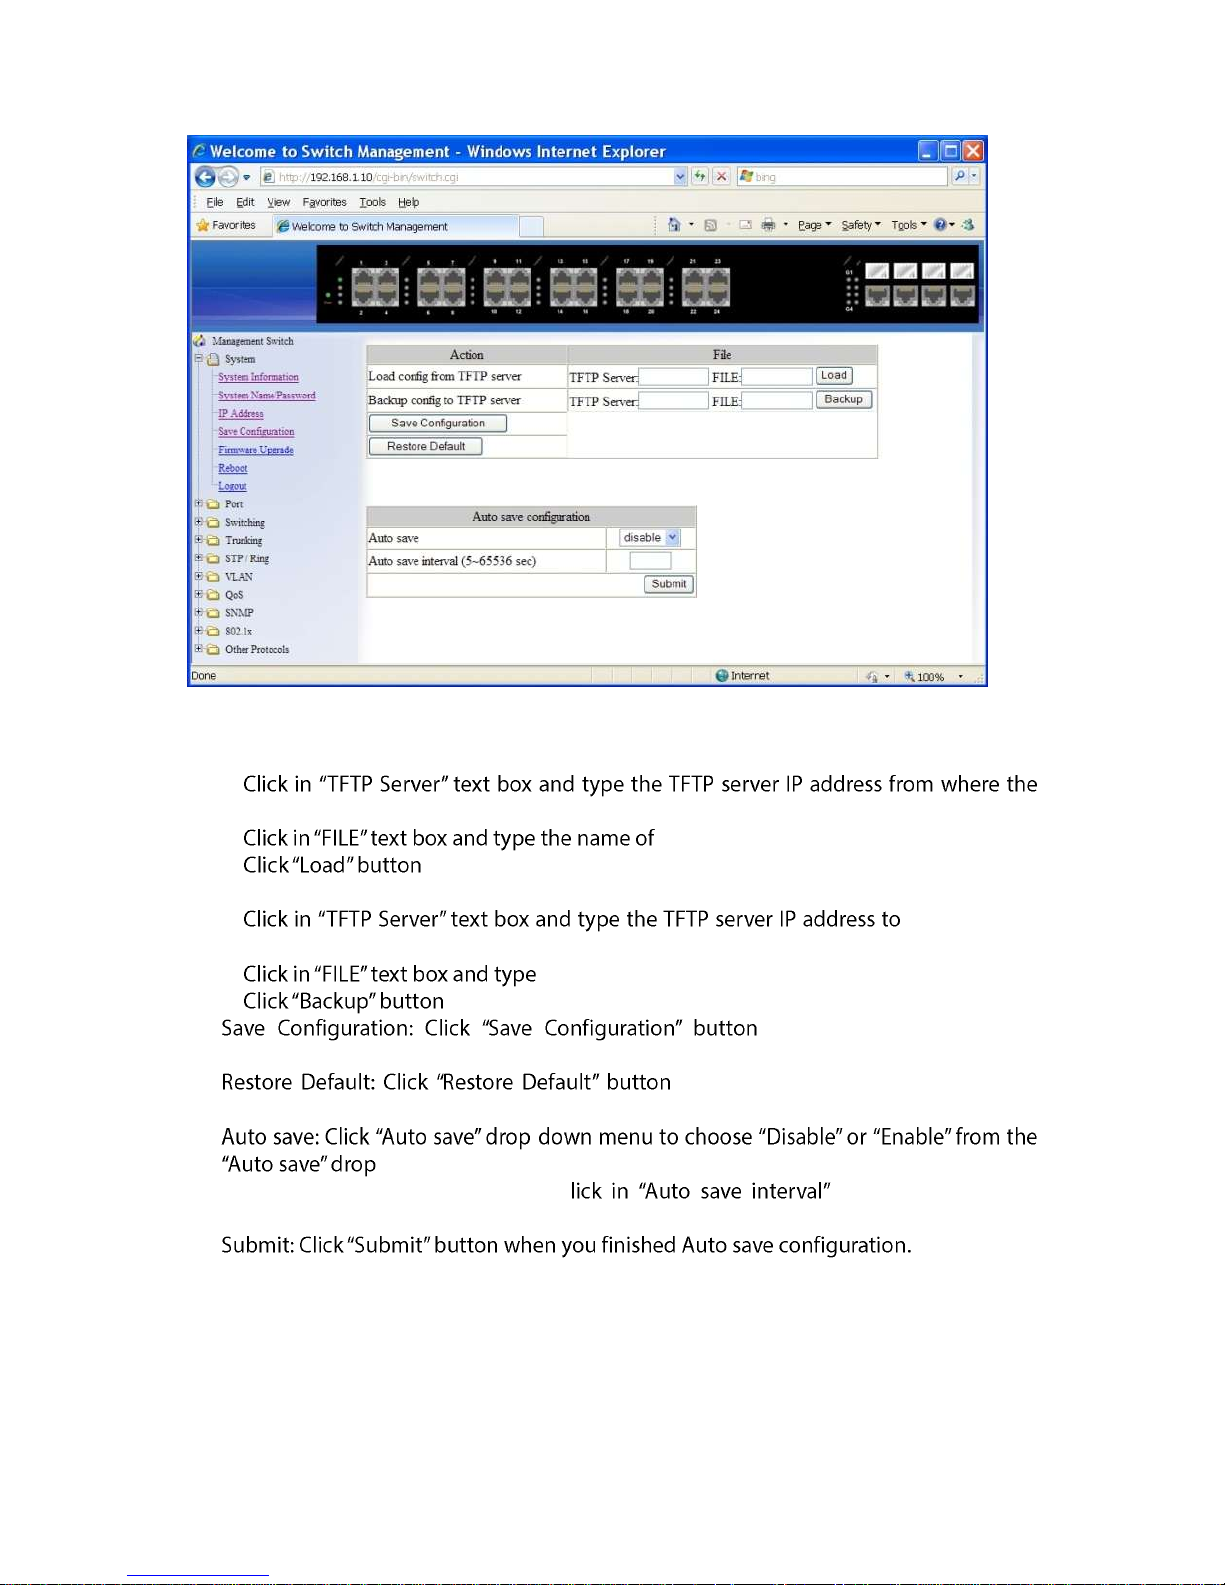
Save Configuration
1. Load config from TFTP server:
file will be obtained.
the file that will be obtained.
to load the file from the TFTP server.
2. Backup config to TFTP server:
where the file
will be backup.
the name of the file that will be backup.
to backup the file to the TFTP server.
3. to save your configuration
settings.
4. to restore the default settings of the
switch.
5. -
-down list to disable or enable Auto save for the switch.
6. Auto save interval (5~65536 sec): C text box and type a
decimal number between 5 and 65536.
7.
Page 34
User Manual Page 34
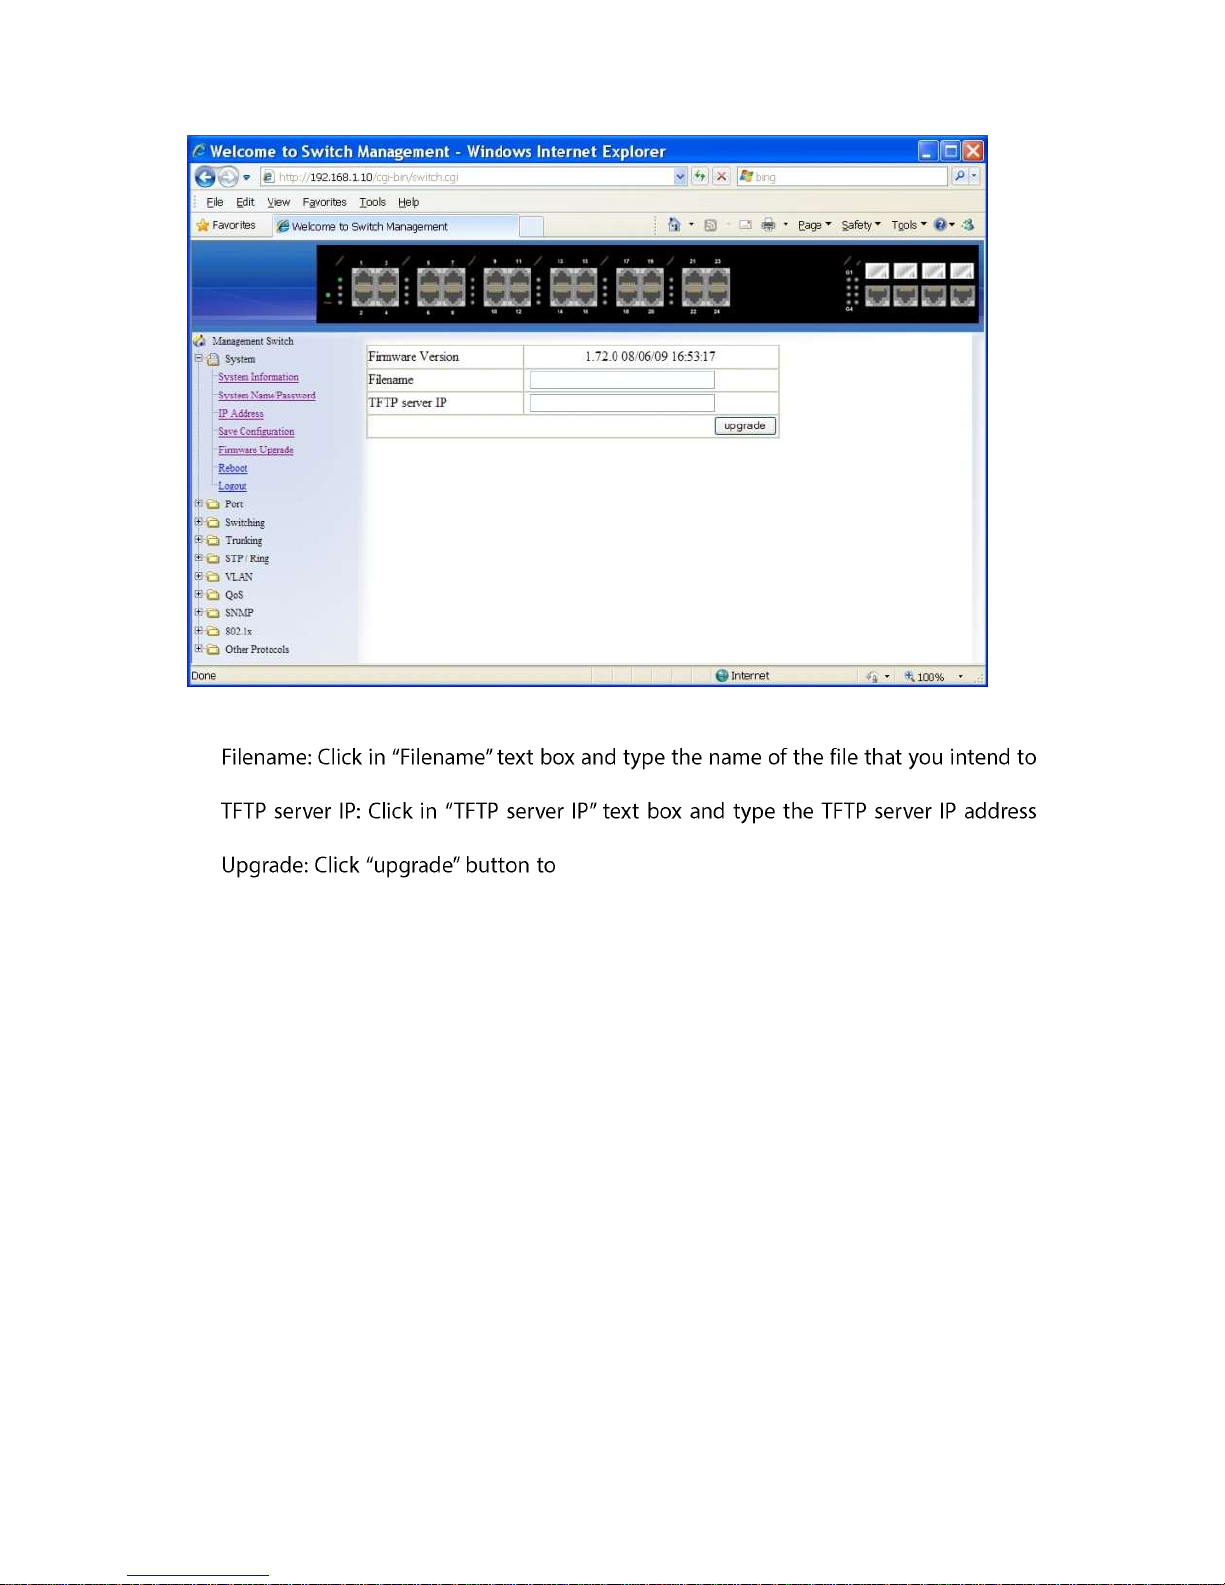
Firmware Upgrade
1.
upgrade it to the switch.
2.
from where the file will be obtained.
3. upgrade firmware to the switch. Please follow the
message on the screen during the firmware upgrade process. Do not turn off the
power or perform other functions during this period of time. Reboot the switch after
completing the upgrade process.
Page 35
User Manual Page 35
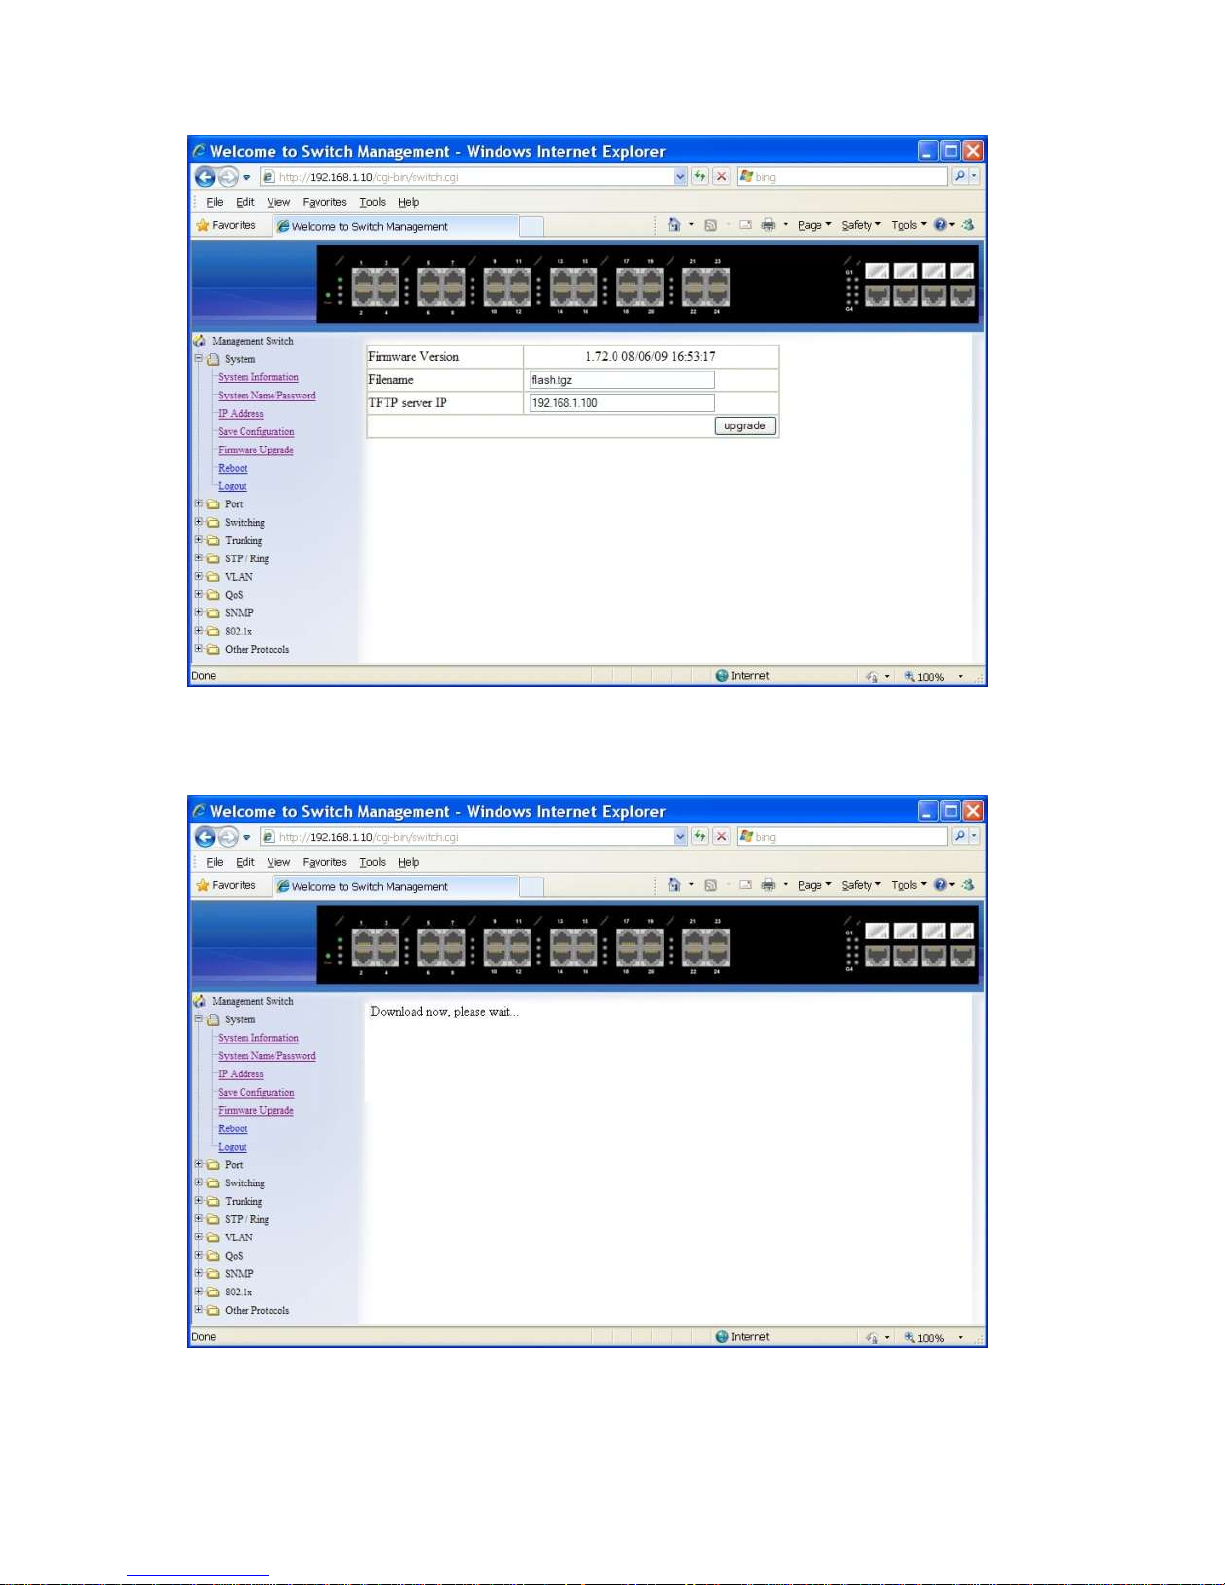
Please follow the message on the screen during the firmware upgrade process. Do not
turn off the power or perform other functions during this period of time.
Page 36
User Manual Page 36
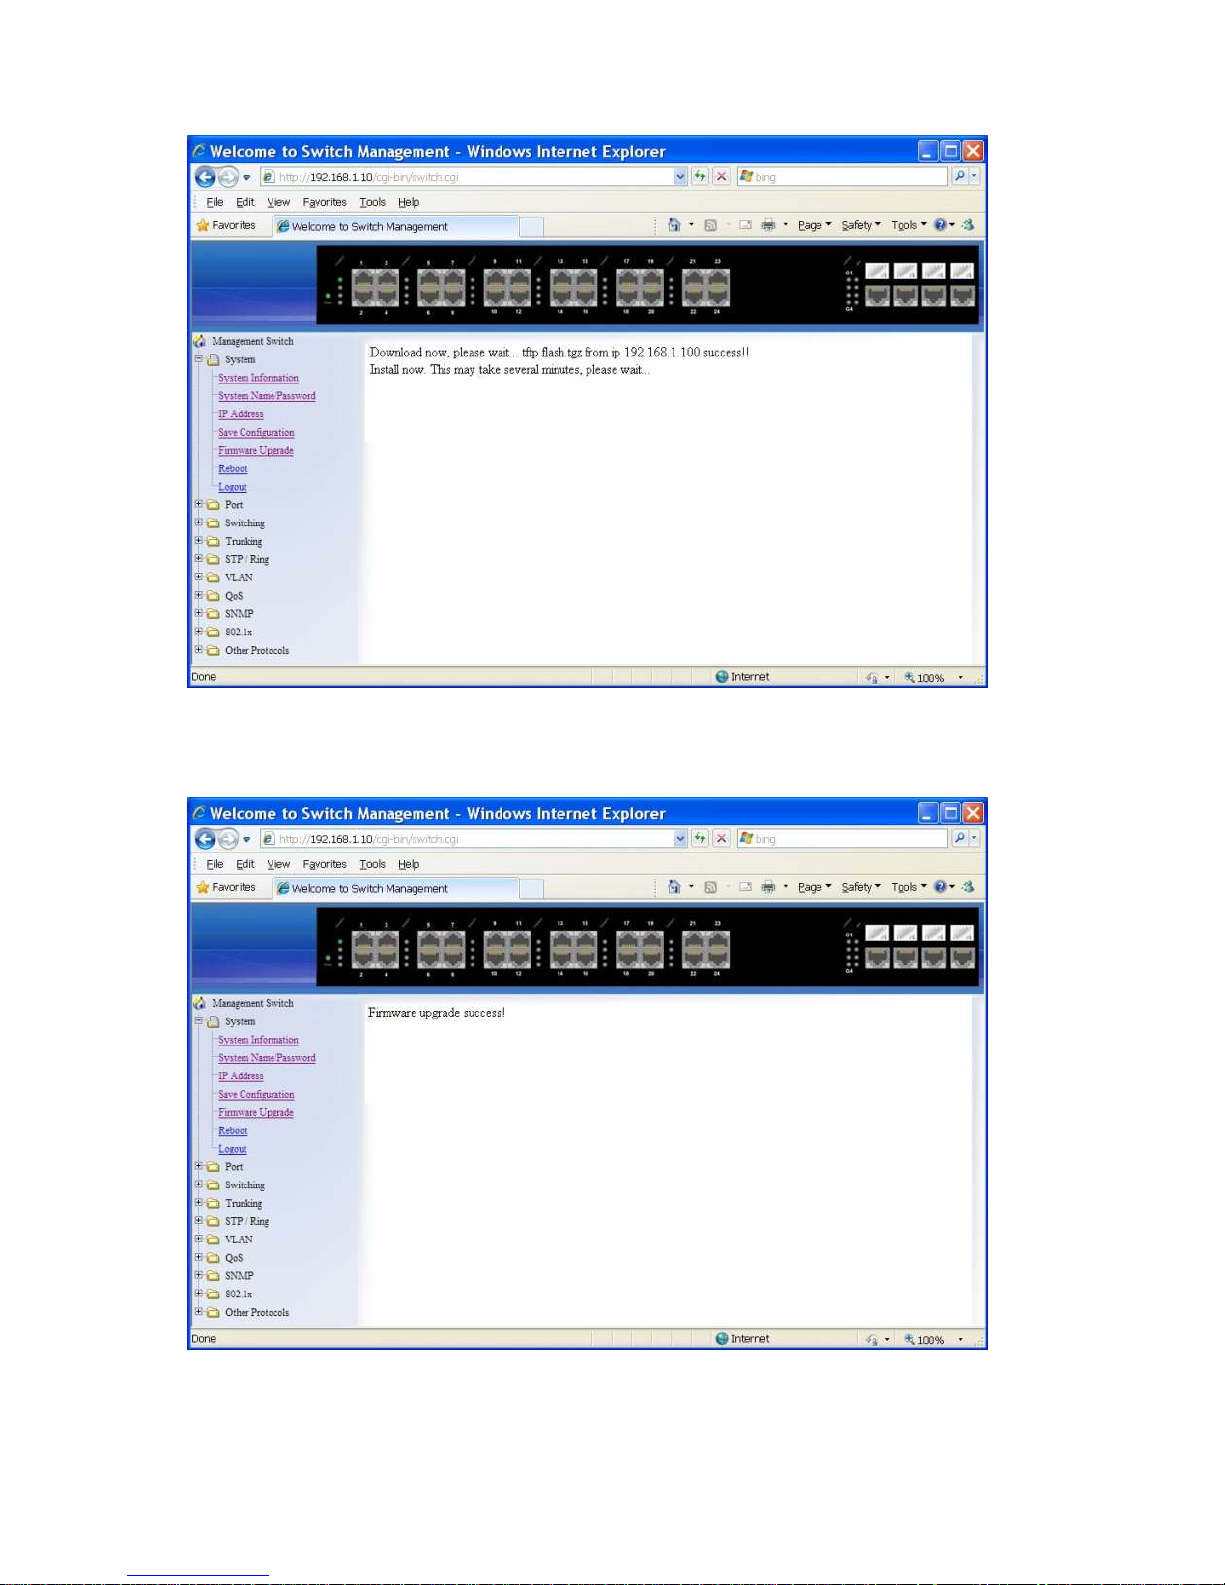
Firmware has been upgraded successfully to the switch. Reboot the switch after
completing the upgrade process.
Page 37
User Manual Page 37
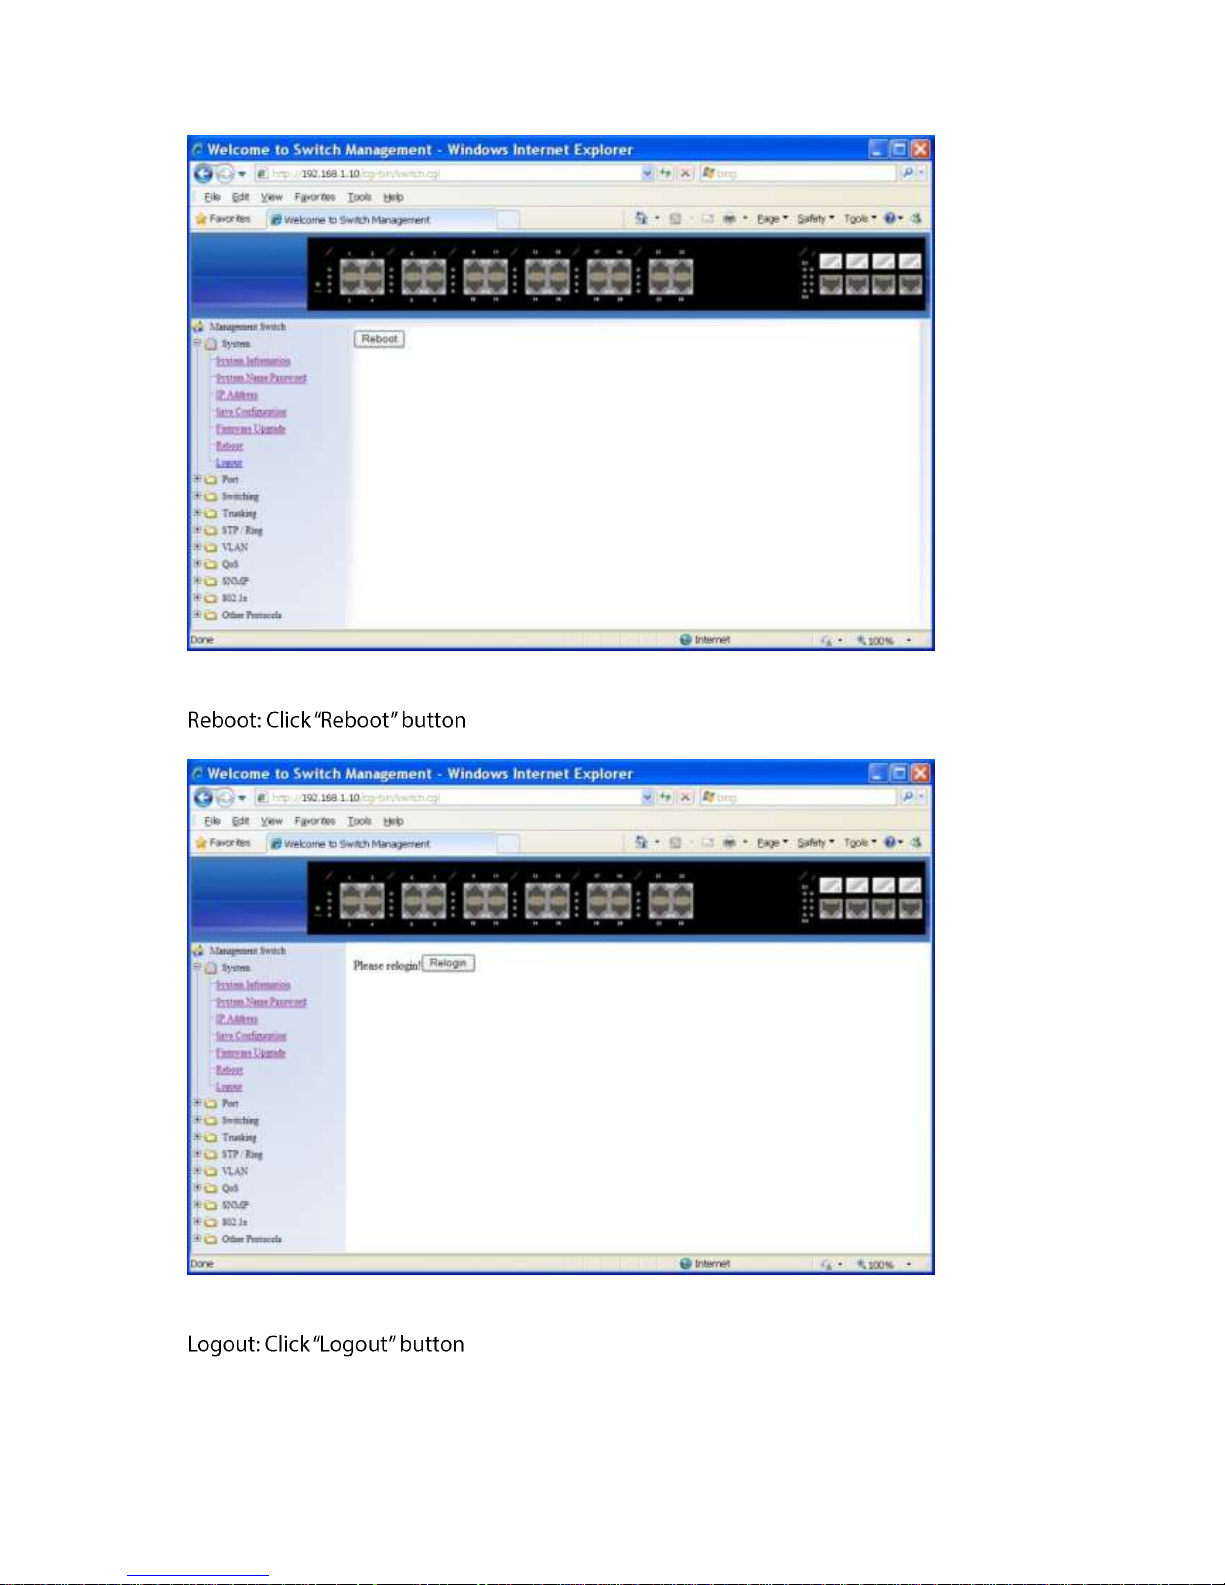
Reboot
to restart the switch.
Logout
to logout of the switch.
Page 38
User Manual Page 38
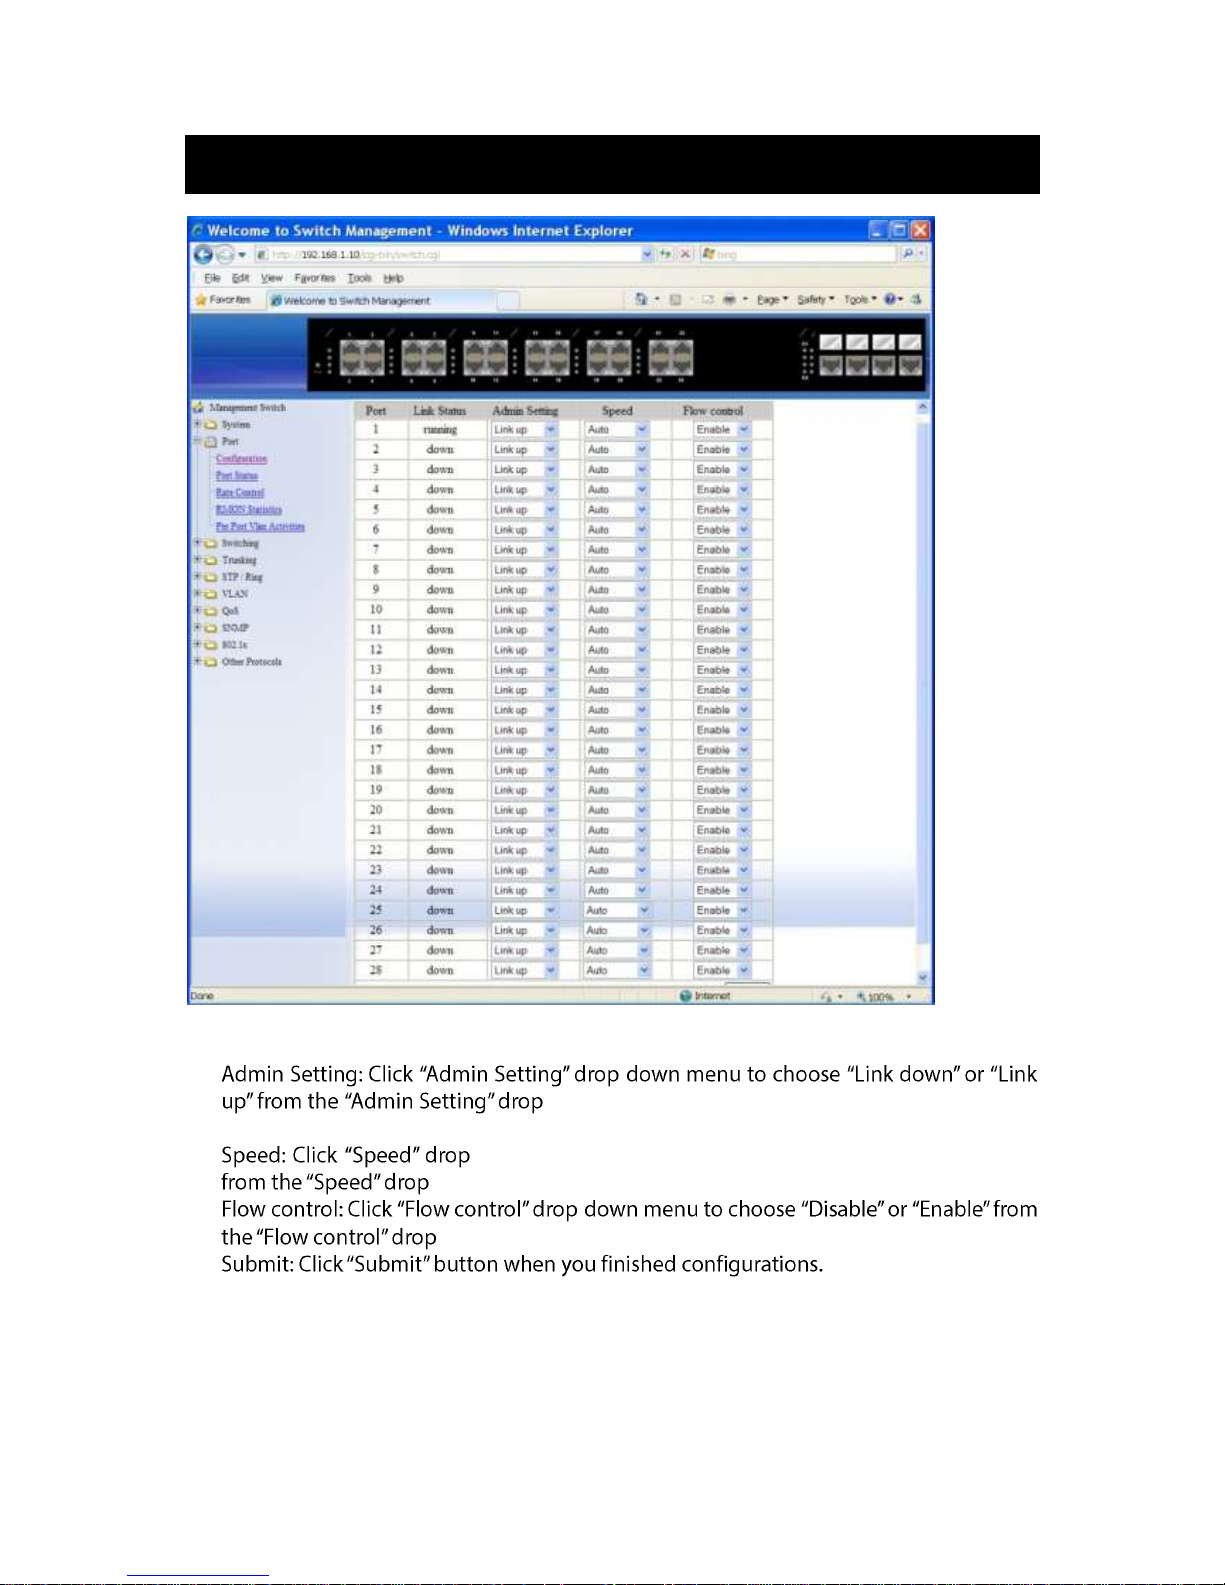
Port
Configuration
1. -
-down list to disable or enable Admin Setting for the
port.
2. -down menu to change the line speed and duplex settings
-down list for the port.
3. -
-down list to disable or enable Flow control for the port.
4.
Page 39
User Manual Page 39
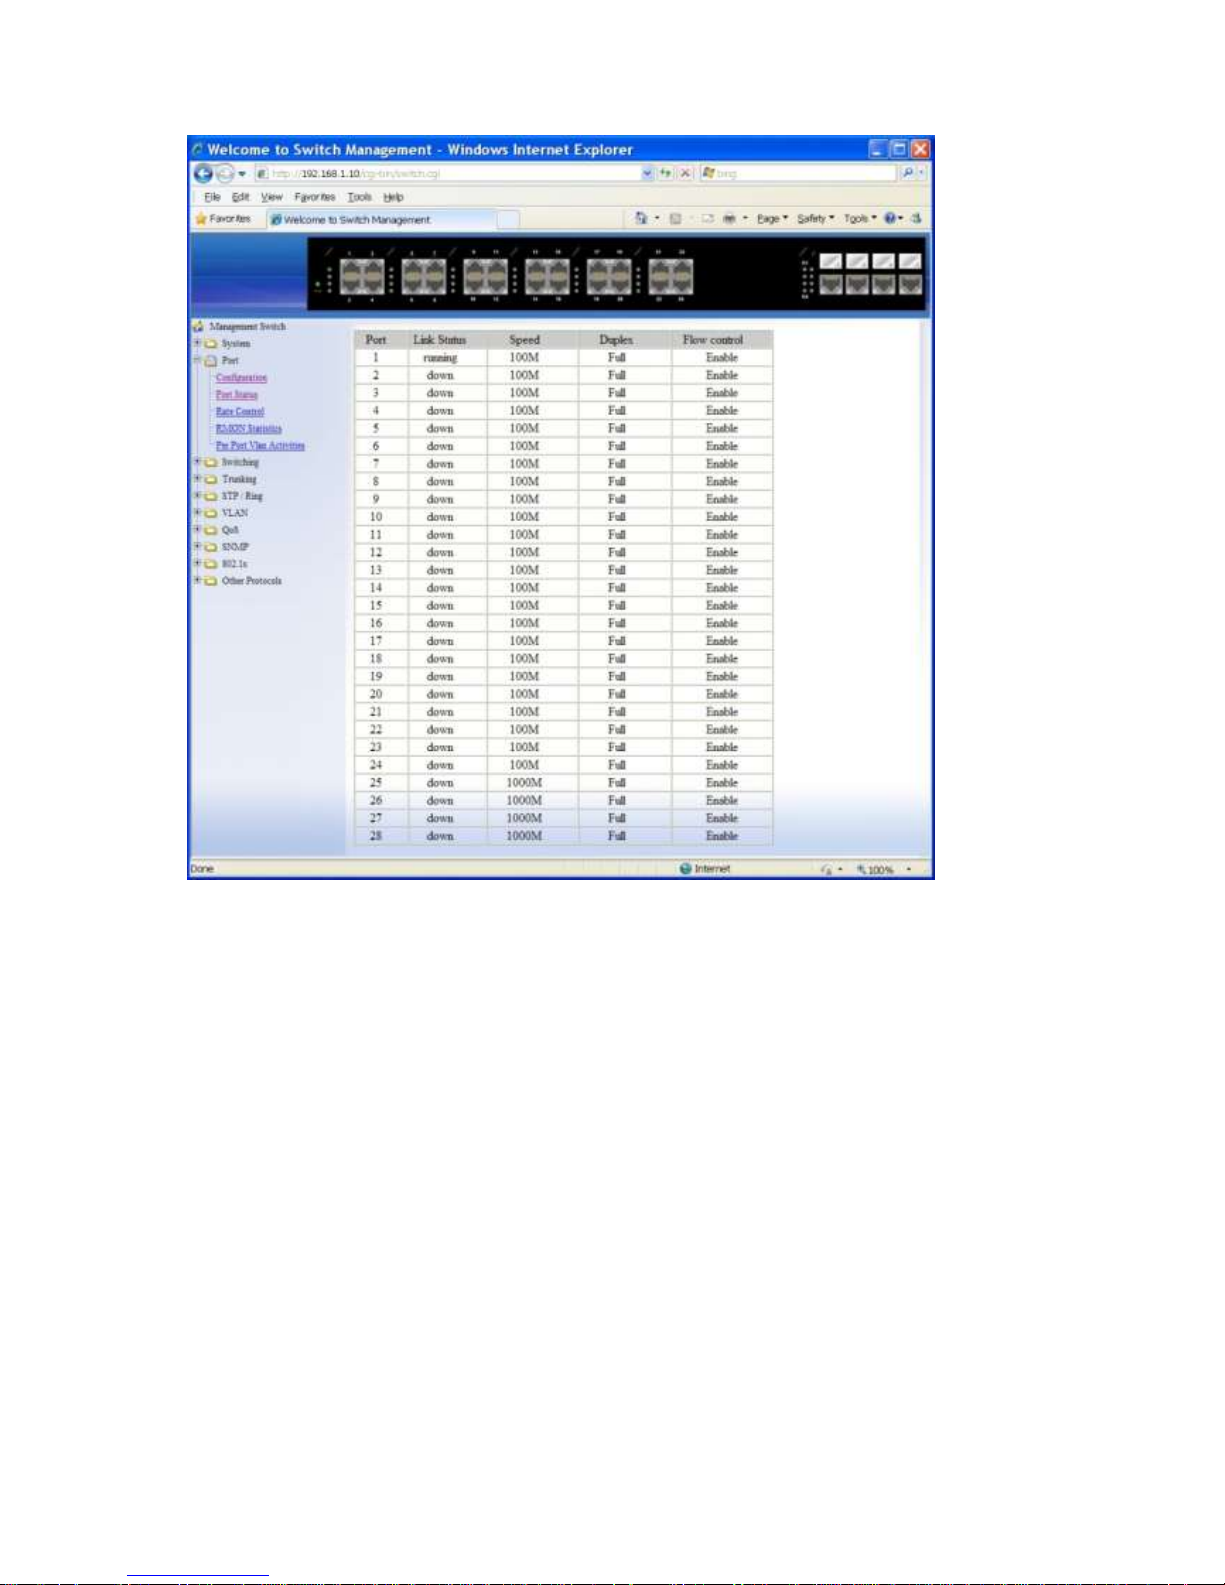
Port Status
View the Link Status, Speed, Duplex, and Flow control status for all ports.
Page 40
User Manual Page 40
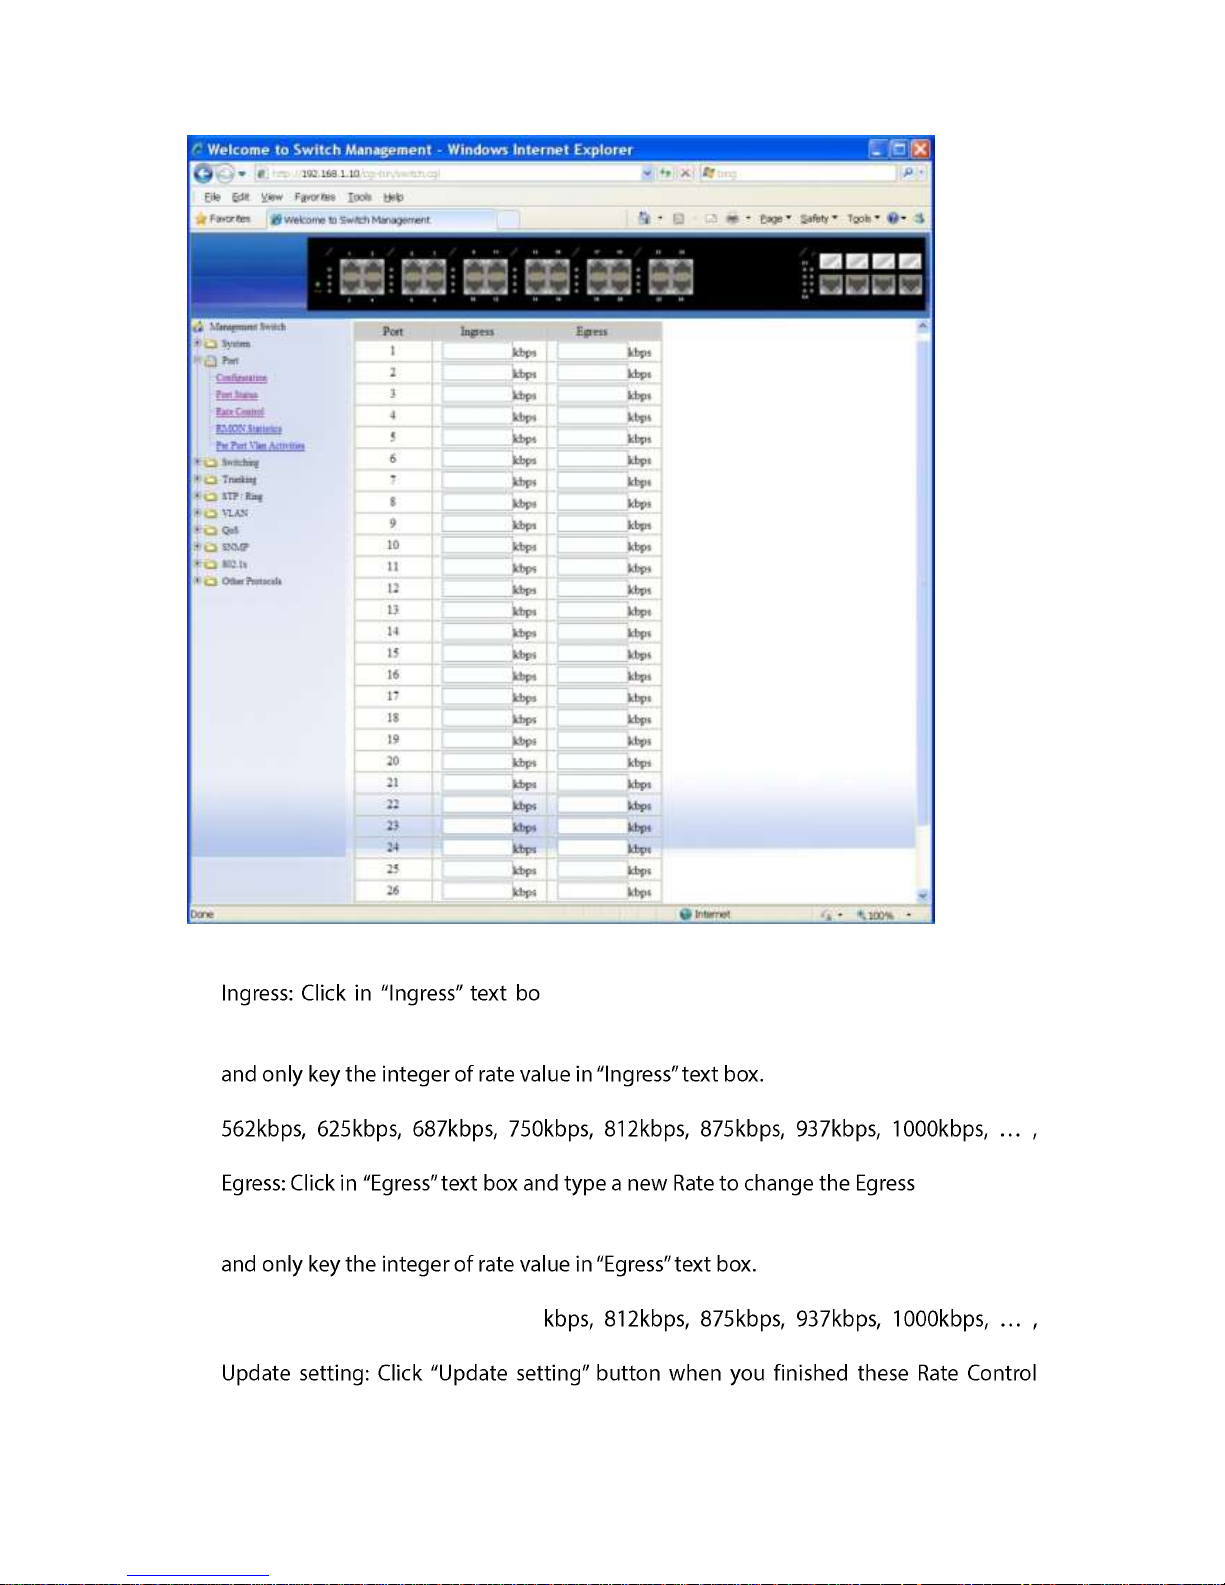
Rate Control
1. x and type a new Rate to change the Ingress Rate
Control for the port.
The rate value is a multiple of 62.5kbps. Please round off decimal fraction of rate value
Rate Values: 62kbps, 125kbps, 187kbps, 250kbps, 312kbps, 375kbps, 437kbps, 500kbps,
1000000kbps.
2. Rate Control
for the port.
The rate value is a multiple of 62.5kbps. Please round off decimal fraction of rate value
Rate Values: 62kbps, 125kbps, 187kbps, 250kbps, 312kbps, 375kbps, 437kbps, 500kbps,
562kbps, 625kbps, 687kbps, 750
1000000kbps.
3.
settings.
Page 41
User Manual Page 41
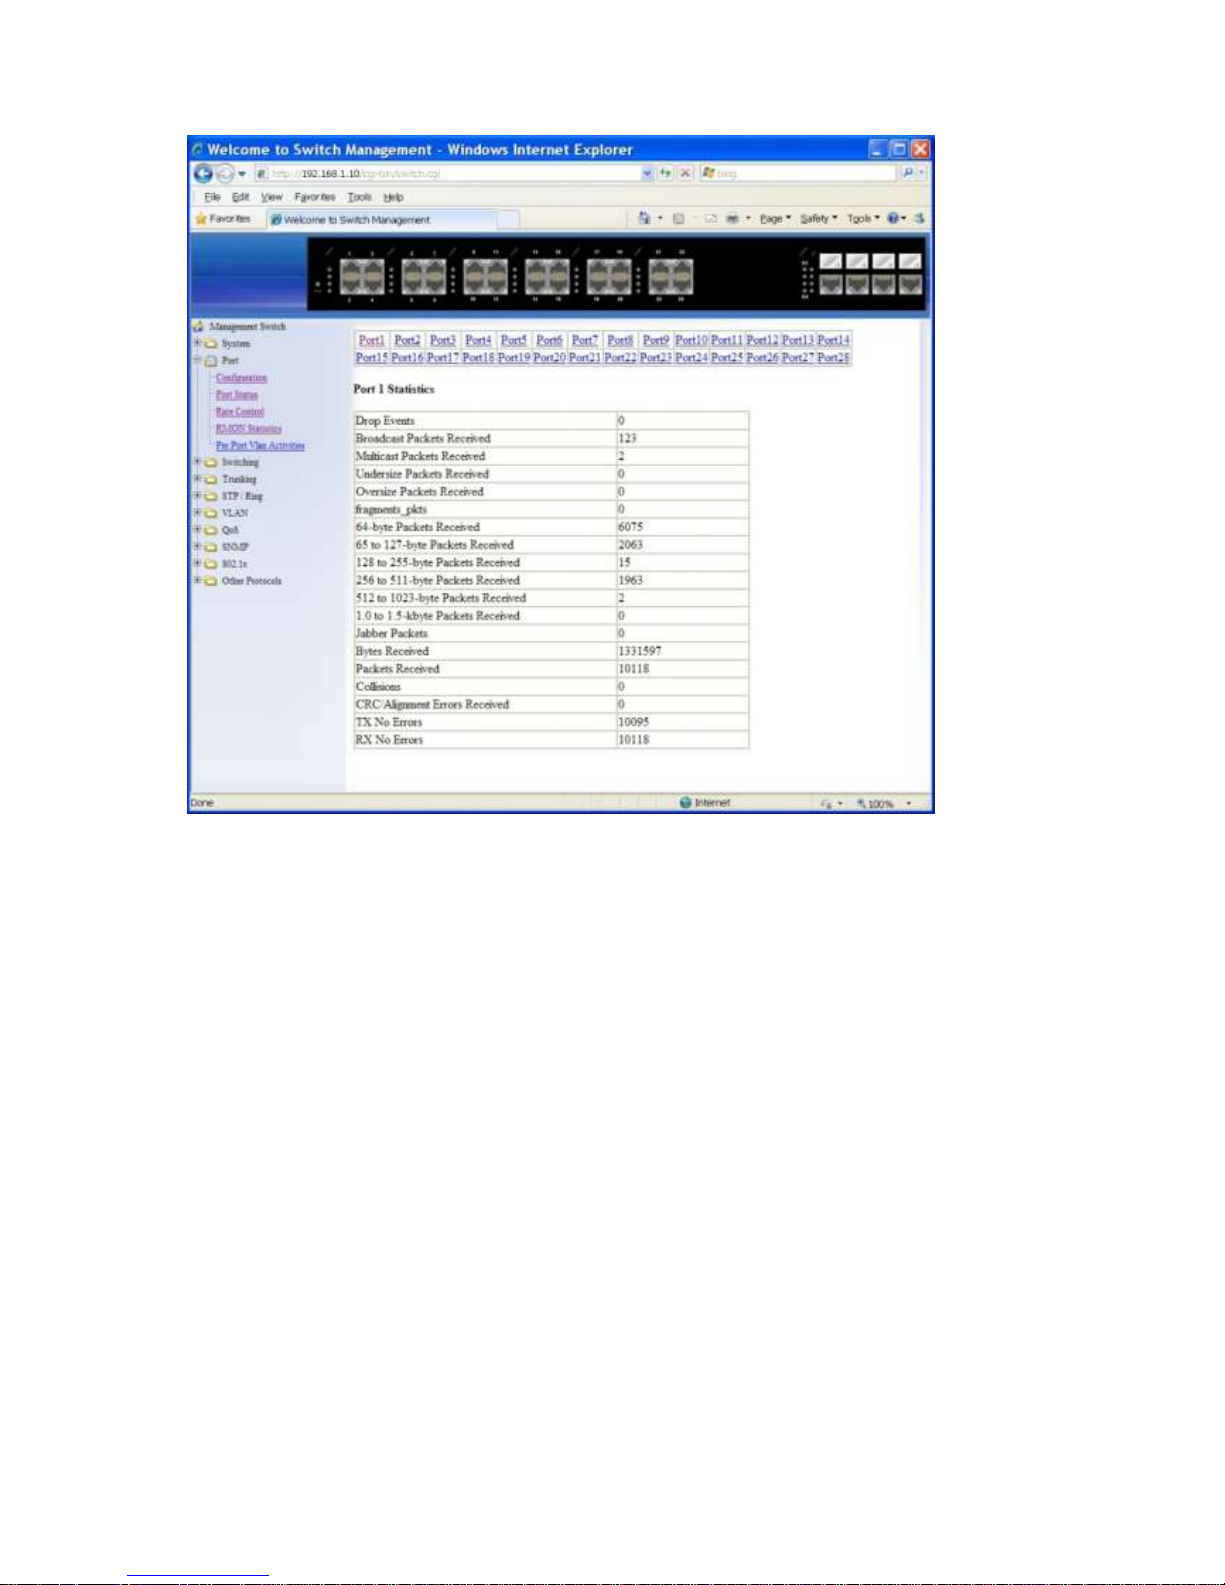
RMON Statistics
Click Port 1 ~ Port 28 to view corresponding RMON Statistics.
Page 42
User Manual Page 42
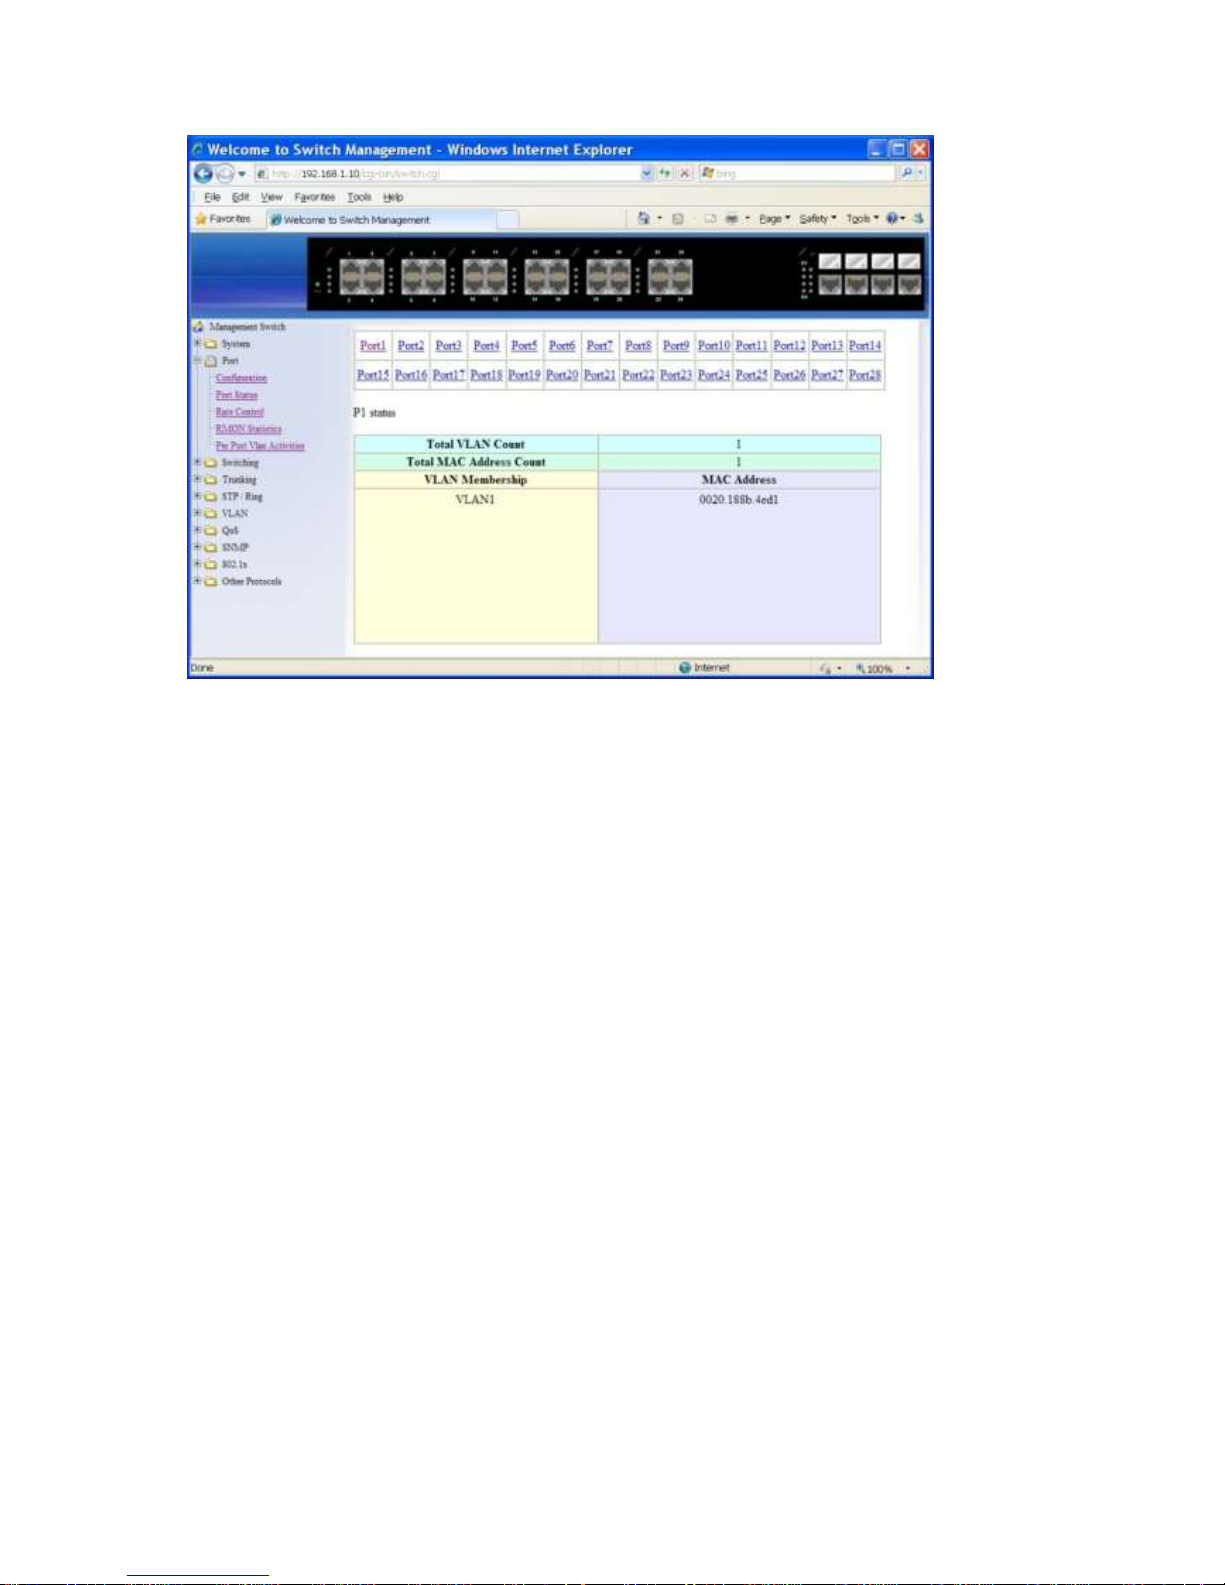
Per Port Vlan Activities
Click Port 1 ~ Port 28 to view corresponding vlan activities.
Page 43
User Manual Page 43
Switching
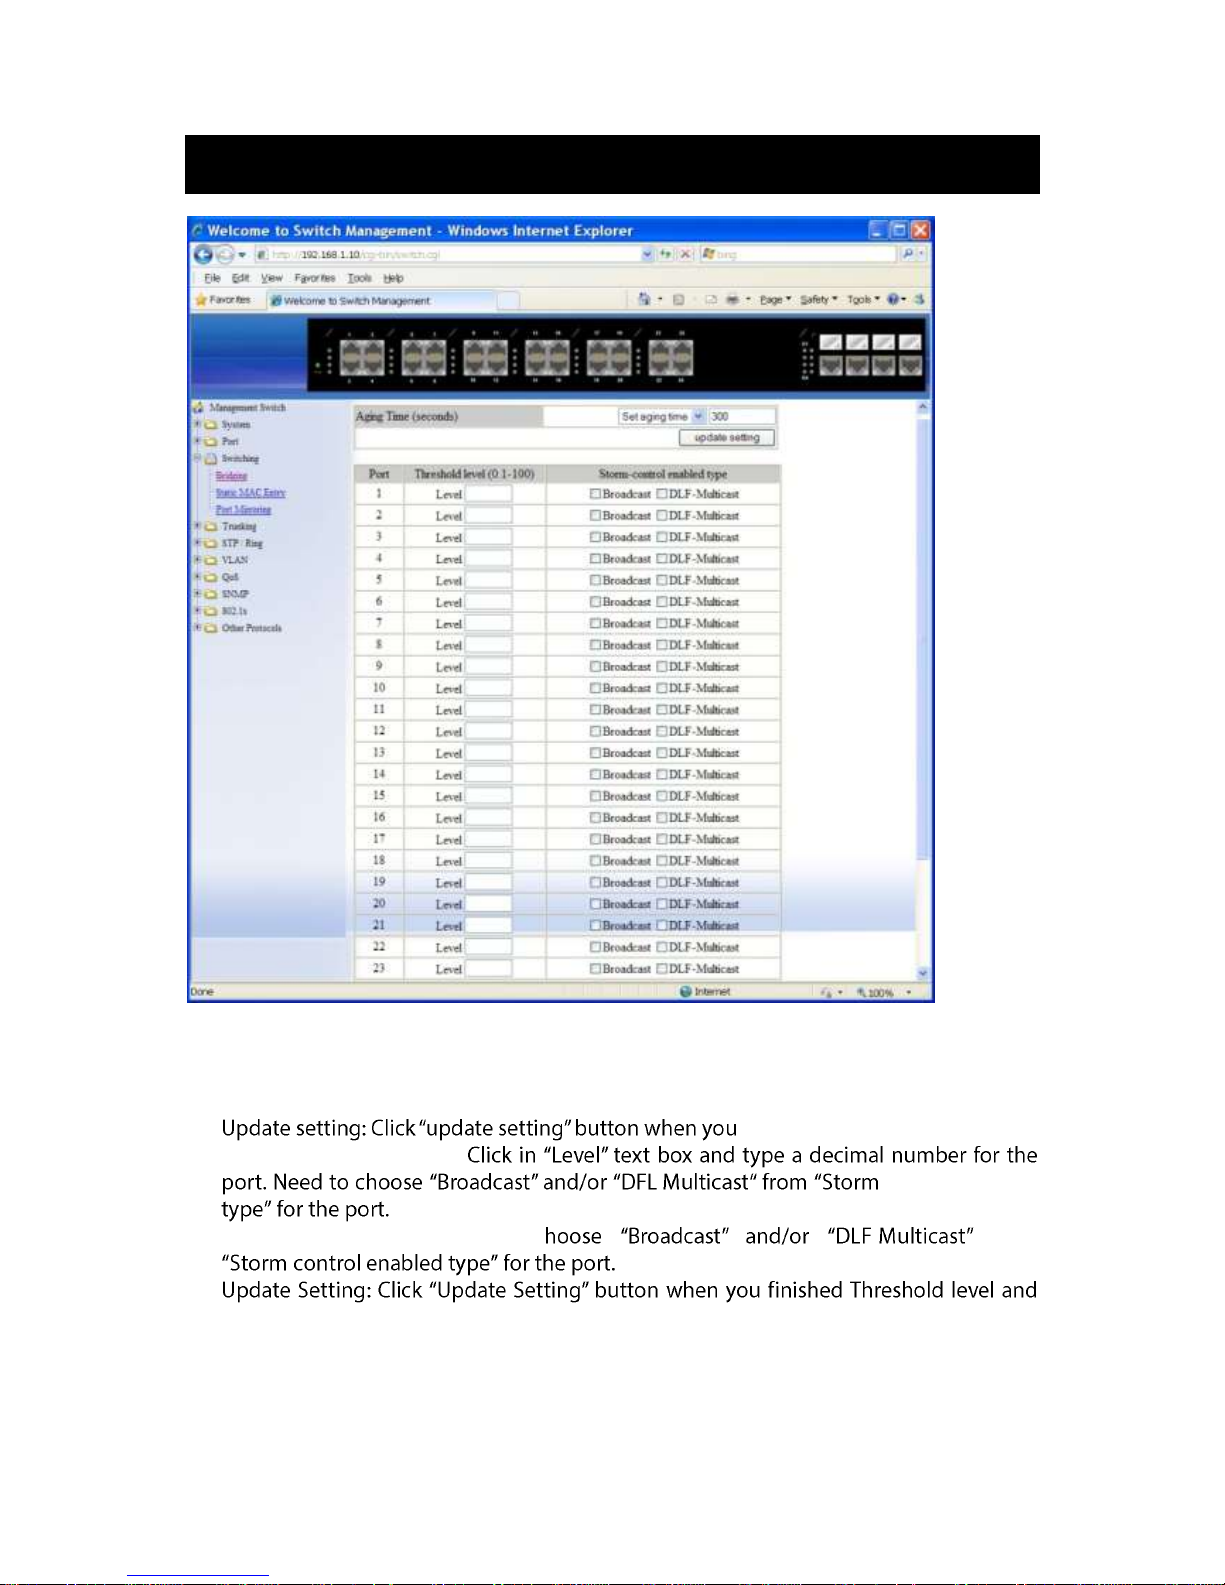
Bridging
1. Aging Time (seconds): Click the text box and type a decimal number as Bridging Aging
Time in seconds.
2. finished Aging Time settings.
3. Threshold level (0.1-100):
- -control enabled
DLF (Destination Lookup Failure).
4. Storm-control enabled type: C - from
-
5.
Storm-control enabled type settings.
Page 44
User Manual Page 44
Page 45
User Manual Page 45
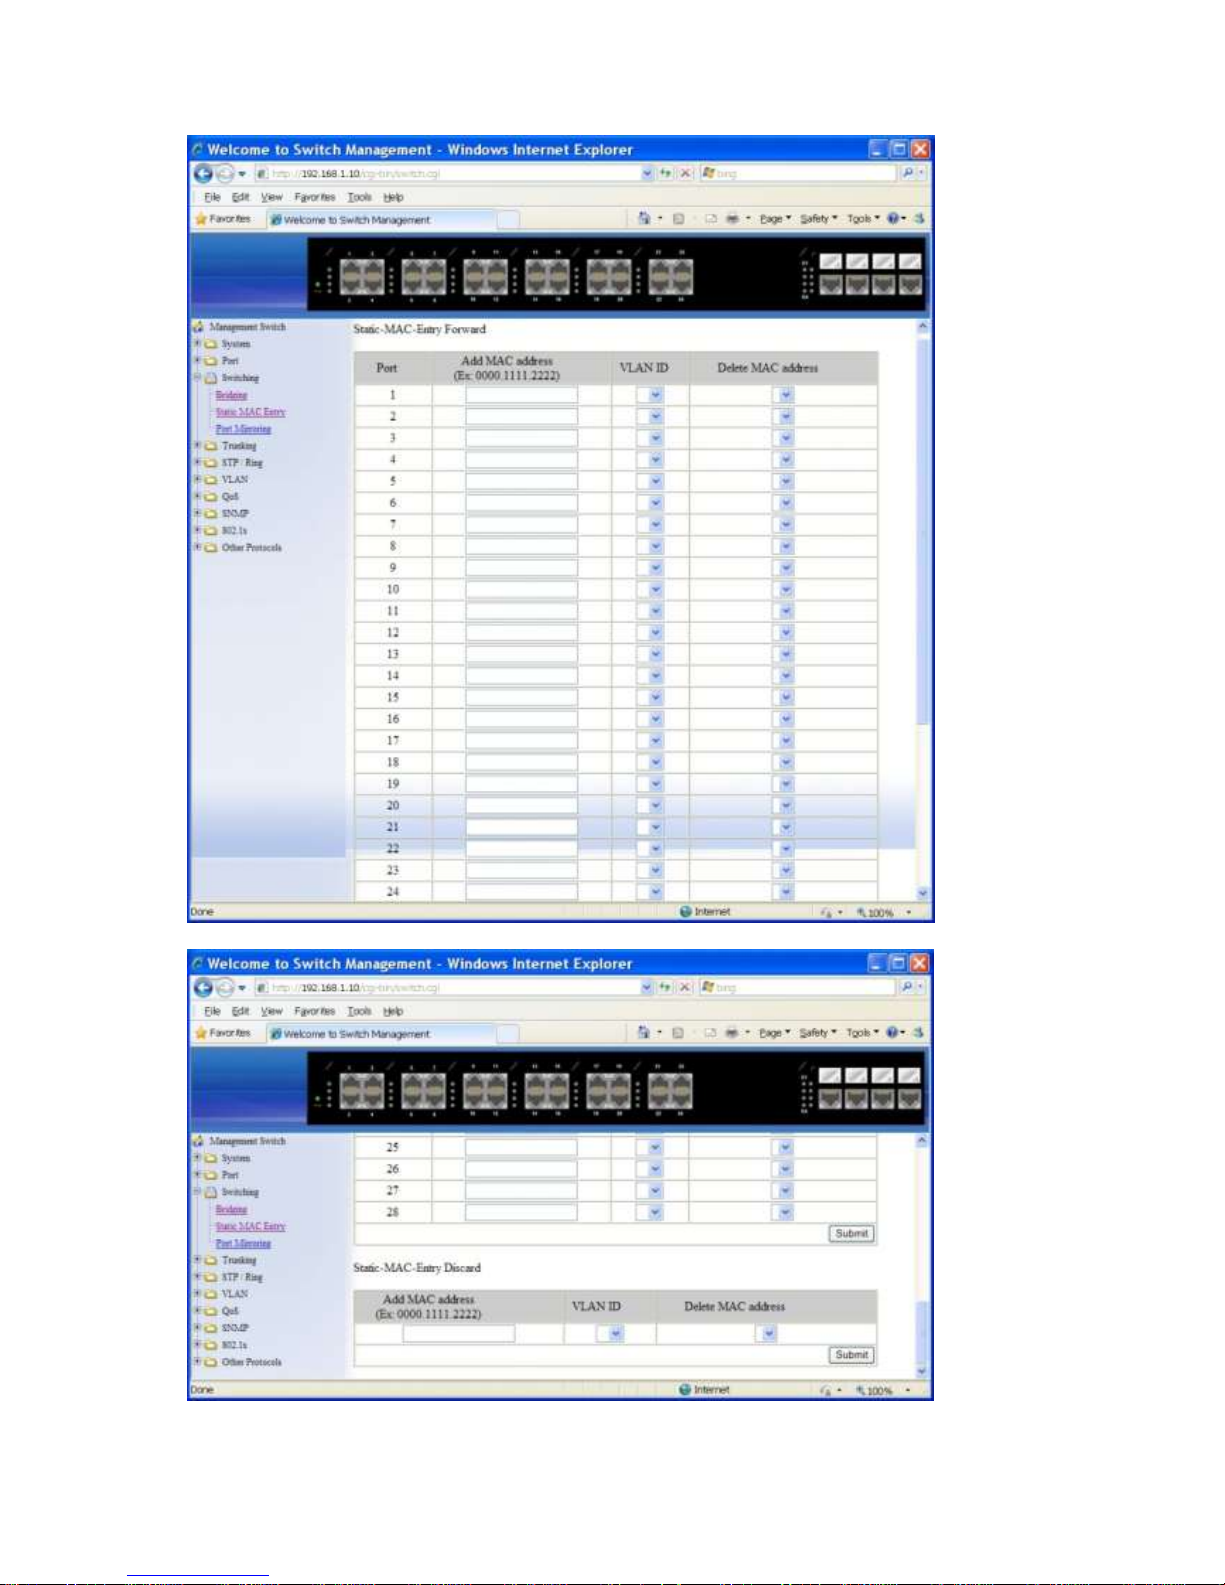
Static MAC Entry
Static-MAC-Entry Forward:
1. Add MAC address: Add MAC address
MAC address for the port.
2. -
drop-down list.
3. Delete MAC address: -down menu and choose a
locked forwarding MAC address -down list to be
deleted from the port.
4. Static-MAC-Entry Forward settings.
Static-MAC-Entry Discard:
1. Add MAC address: Add MAC address MAC address to be
discarded for the VLAN.
2. -down menu and choose a VLAN ID from the
-down list.
3. Delete MAC address: -down menu and choose a MAC
address -down list to be discarded from the VLAN.
4. Static-MAC-Entry Discard settings.
Page 46
User Manual Page 46
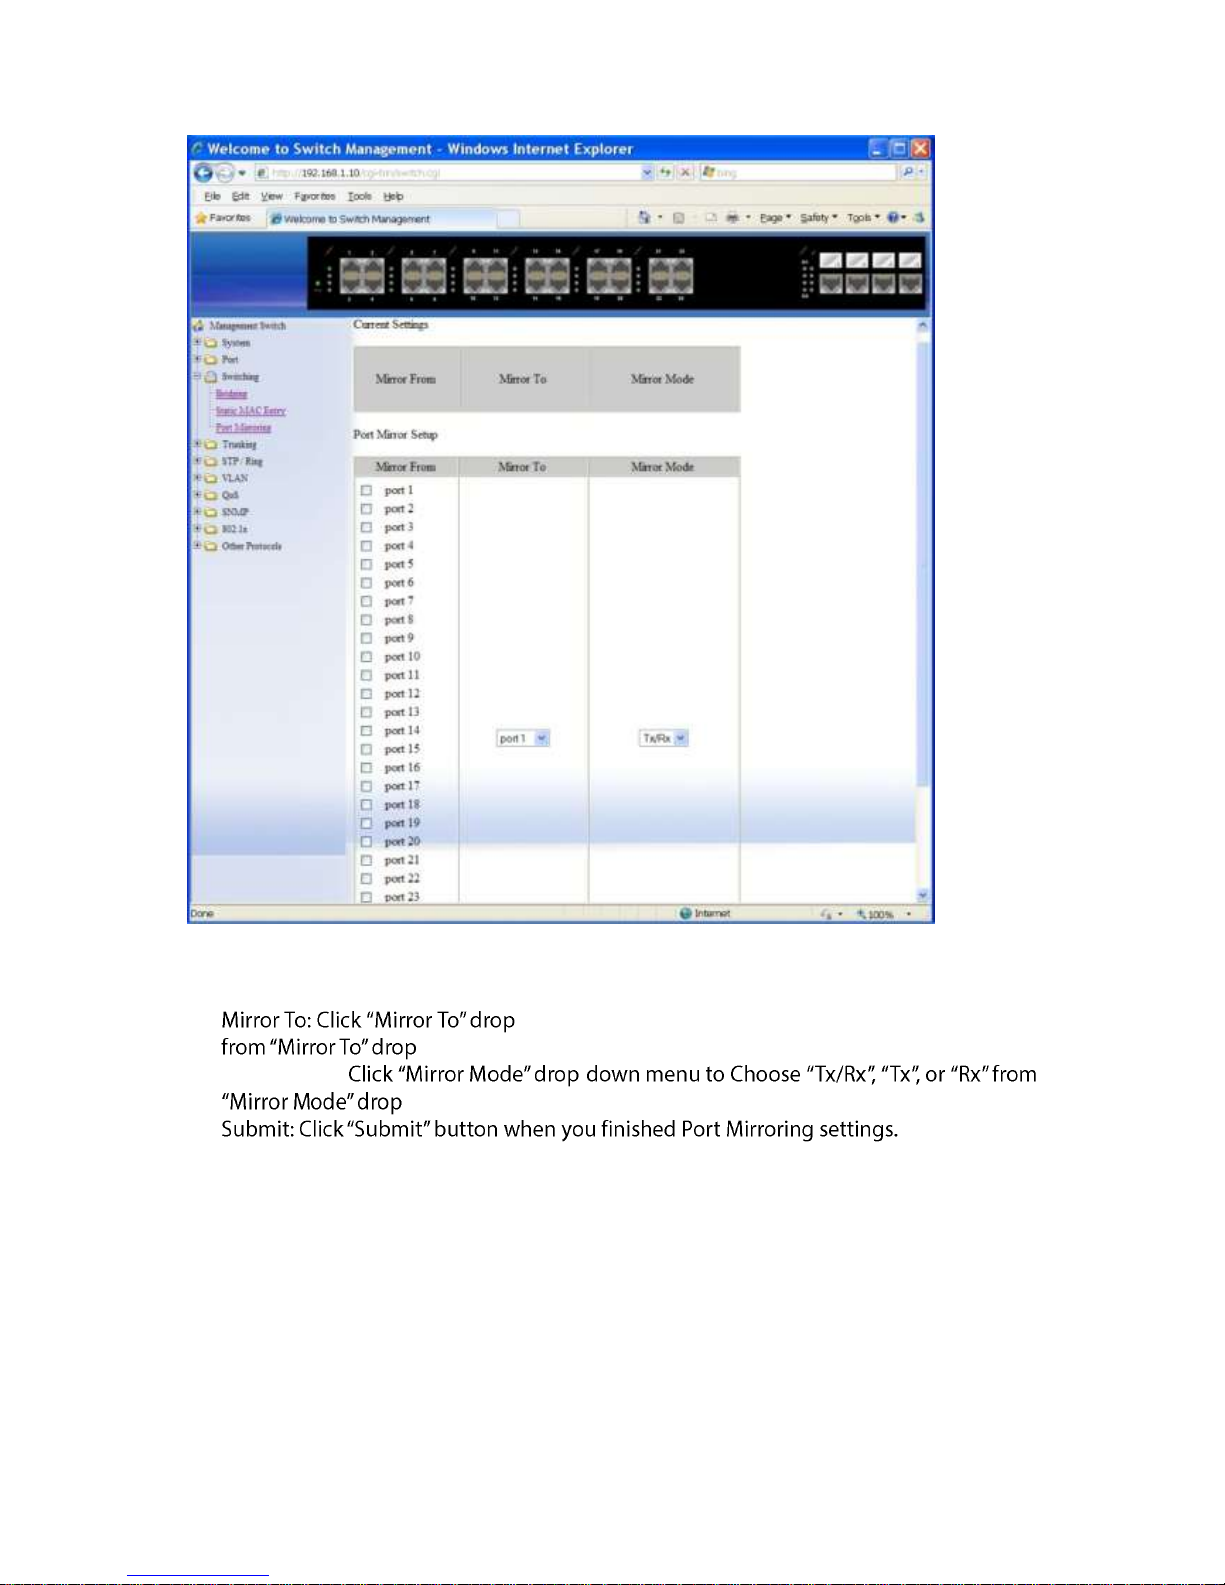
Port Mirroring
1. Mirror From: Choose Mirror From port from Port 1 ~ Port 28.
2. -down menu to Choose Mirror To port (Port 1 ~ Port 28)
-down list.
3. Mirror Mode: -
-down list.
4.
Page 47
User Manual Page 47
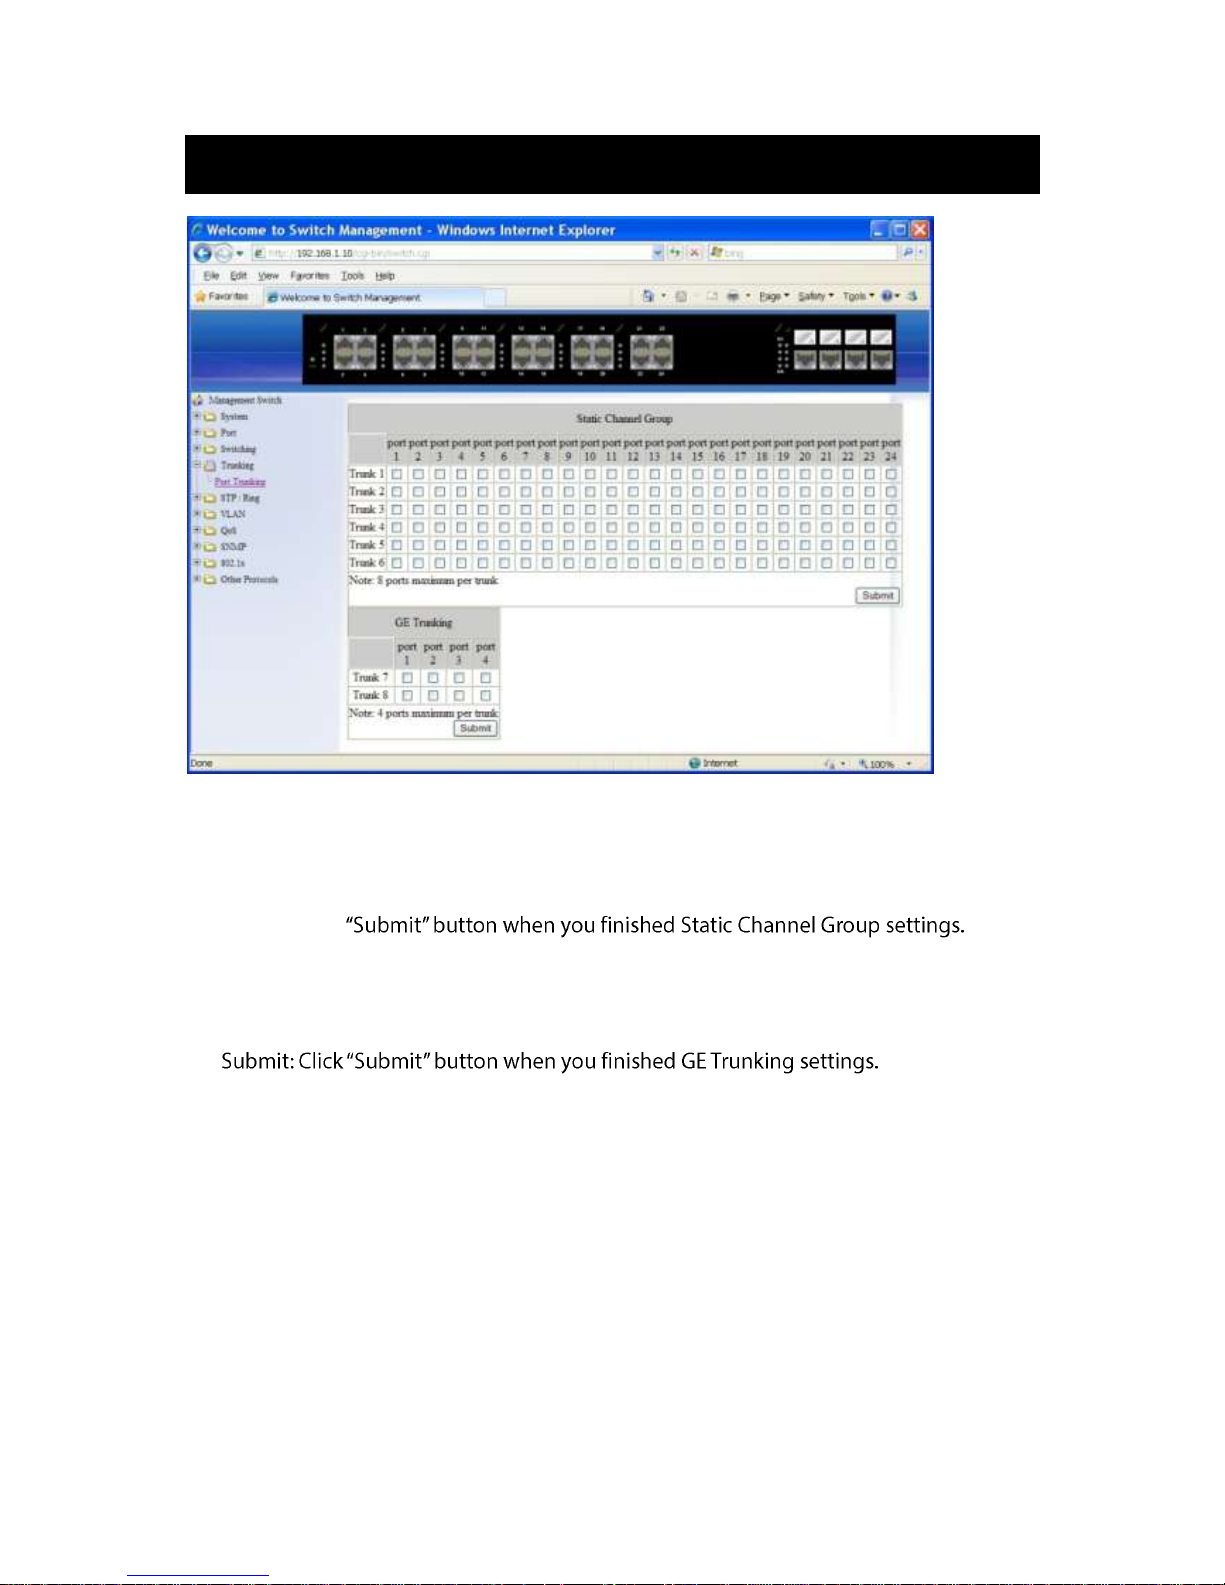
Trunking
Port Trunking
Static Channel Group:
1. Trunk 1 ~ 6: Click Port 1 ~ Port 24 to assign ports to Trunk 1 ~ 6. (Maximum 8 ports per
Trunk.)
2. Submit: Click
GE Trunking:
1. Trunk 7 ~ 8: Click Port 1 ~ Port 4 to assign ports to Trunk 7 ~ 8. (Maximum 4 ports per
Trunk.)
2.
Page 48
User Manual Page 48
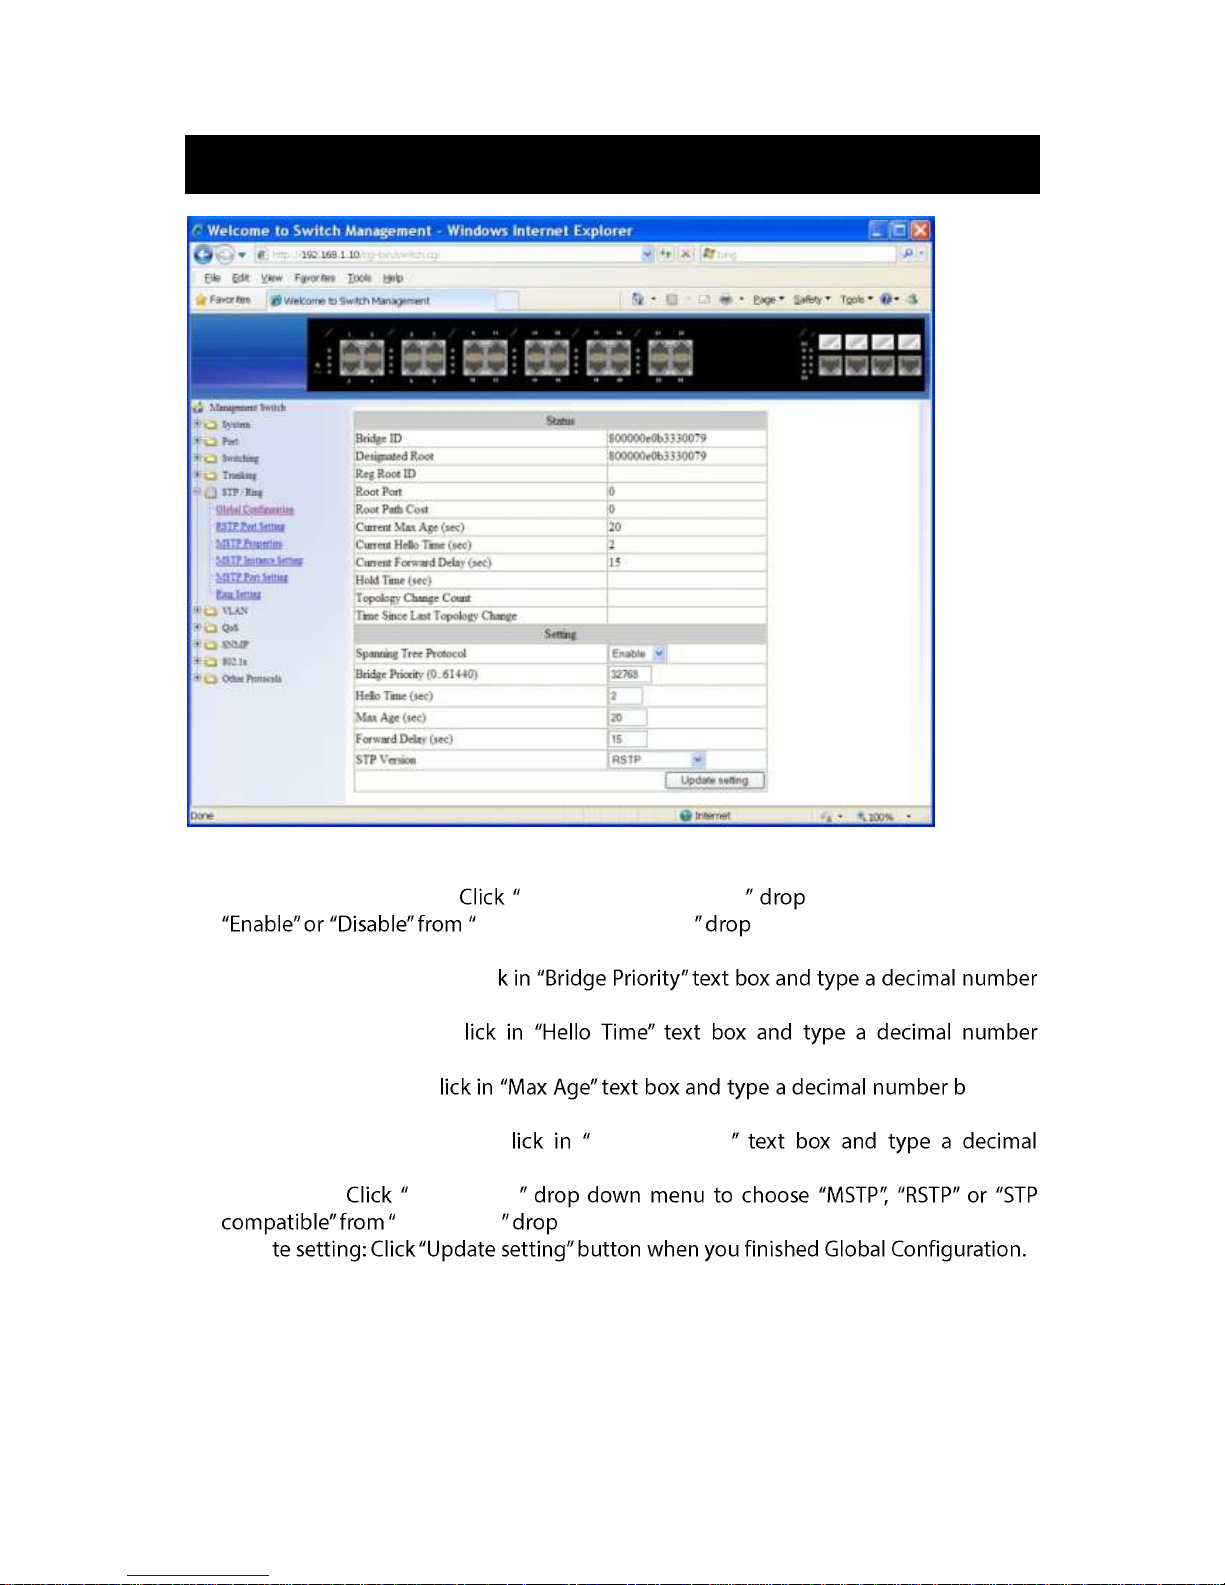
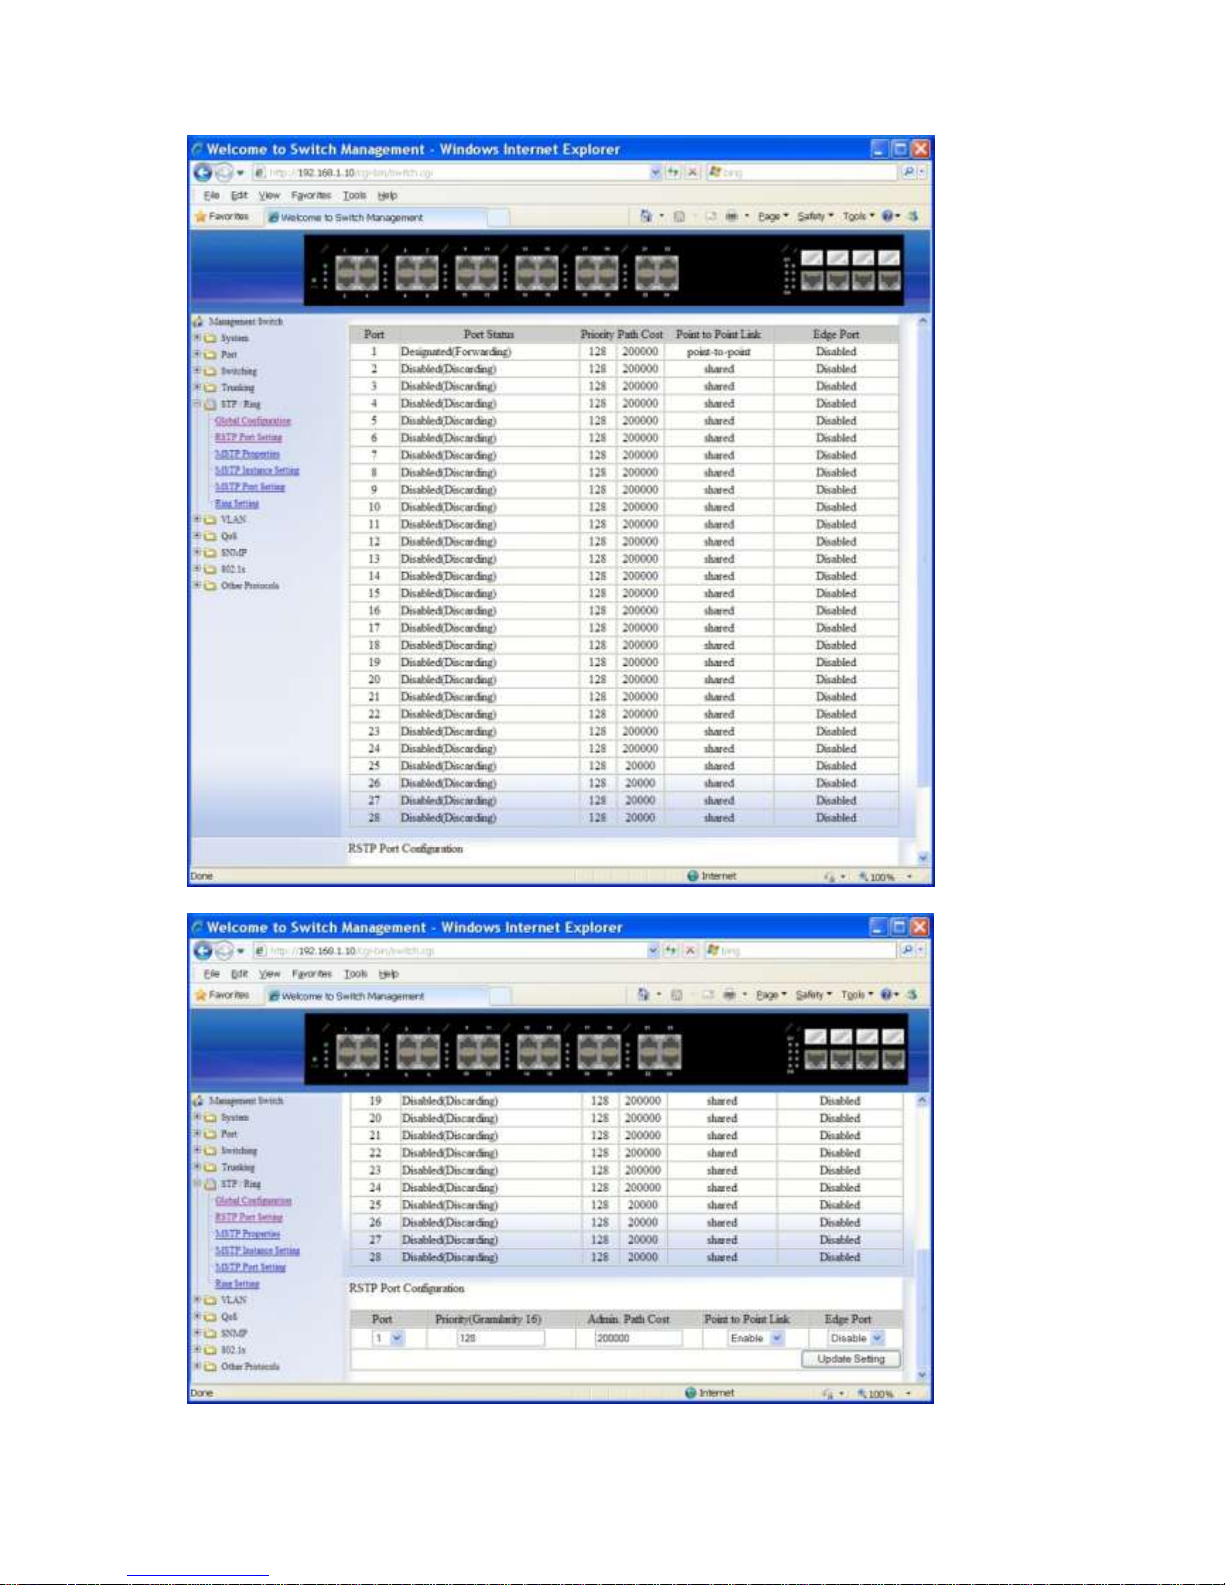
STP / Ring
Global Configuration
1. Spanning Tree Protocol: Spanning Tree Protocol -down menu to Choose
Spanning Tree Protocol -down list to enable or disable
Spanning Tree Protocol.
2. Bridge Priority (0..61440): Clic
between 0 and 61440.
3. Hello Time (sec) (1..9): C
between 1 and 9.
4. Max Age (sec) (6..28): C etween
6 and 28.
5. Forward Delay (sec) (4..30): C Forward Delay
number between 4 and 30.
6. STP Version: STP Version -
STP Version -down list.
7. Upda
Page 49
User Manual Page 49
Page 50
User Manual Page 50
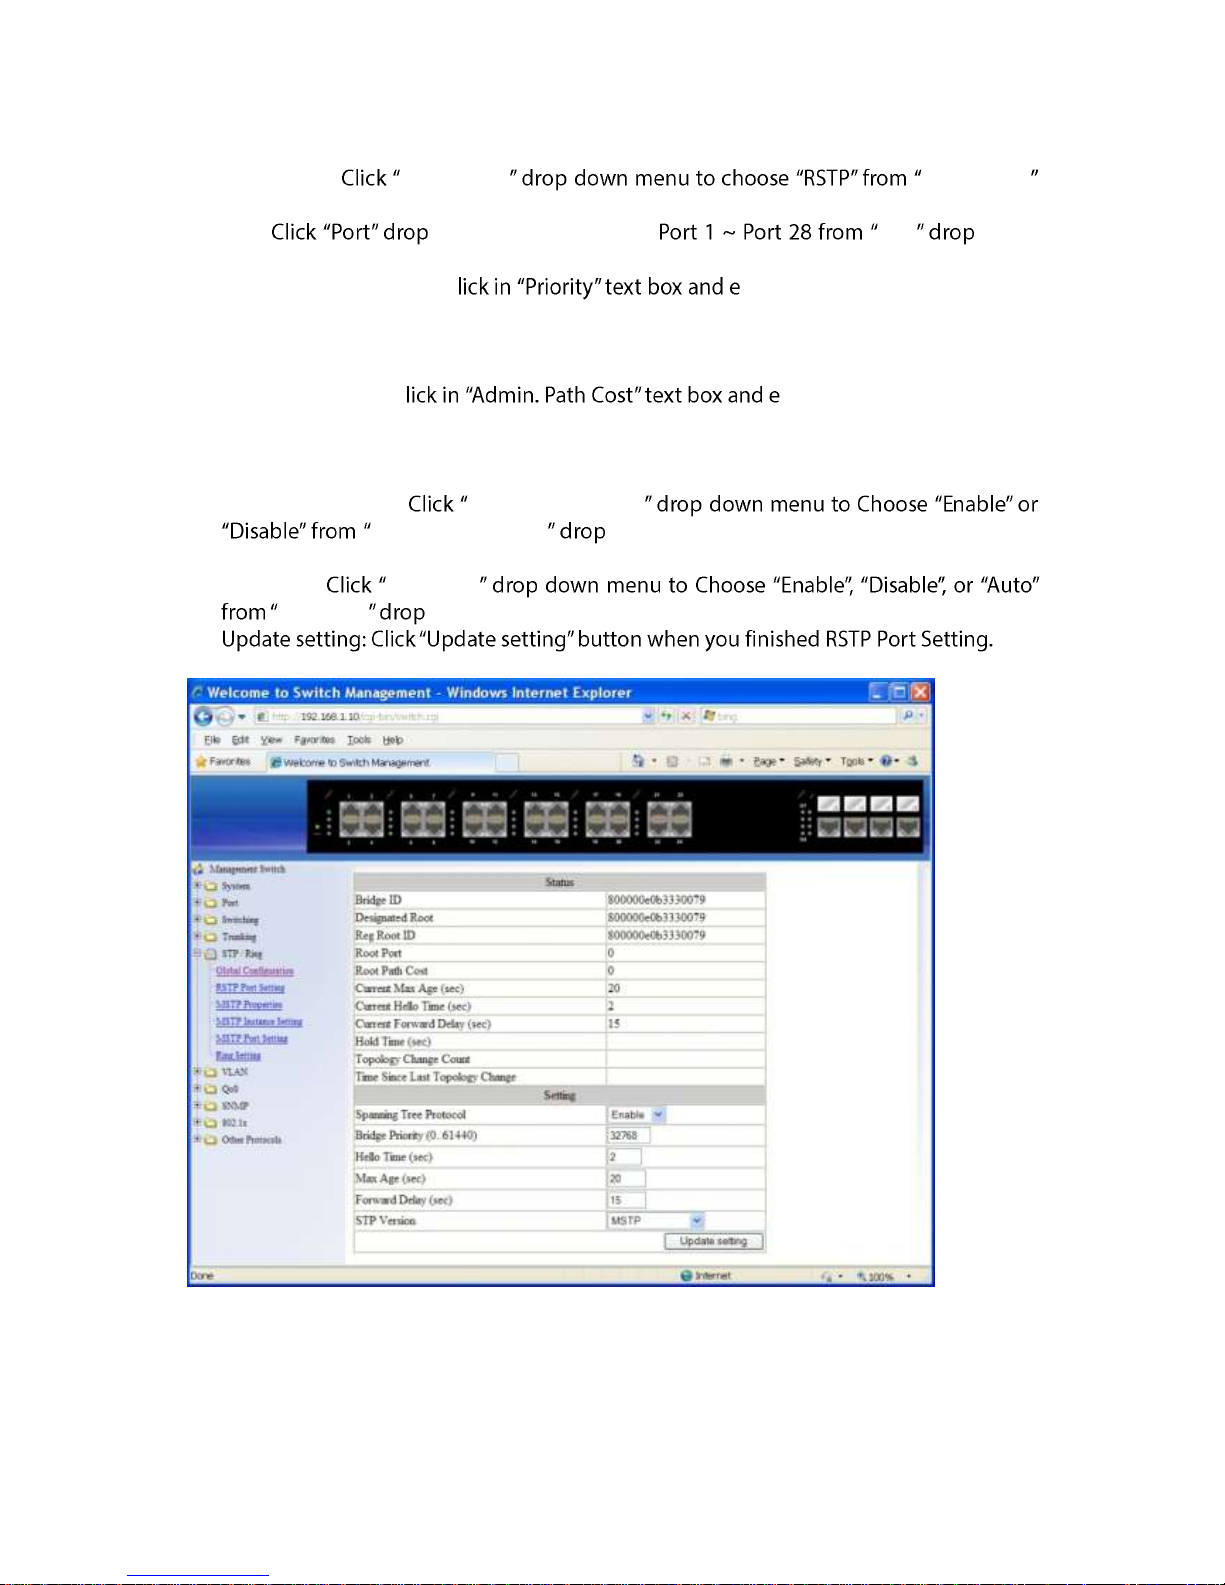
RSTP Port Setting
1. STP Version: STP Version - STP Version
drop-down list.
2. Port: -down menu to choose Port -down
list.
3. Priority(Granularity 16): C nter a value between 0 and 240
to set the priority for the port. A higher priority will designate the port to forward
packets first. A lower number denotes a higher priority. This entry must be divisible by
16. The default priority setting is 128.
4. Admin. Path Cost: C nter a value between 0 and
2000000 to set the Admin. Path Cost for the port. 0 (auto) - Setting 0 for the Admin.
Path Cost will automatically set the speed for forwarding packets to the port for
optimal efficiency. Default port cost: 100Mbps port = 200000. Gigabit port = 20000.
5. Point to Point Link: Point to Point Link -
Point to Point Link -down list to enable or disable Point to Point
Link for the port.
6. Edge Port: Edge Port -
Edge Port -down list to set Enable, Disable, or Auto Edge Port for the port.
7.
Page 51
User Manual Page 51
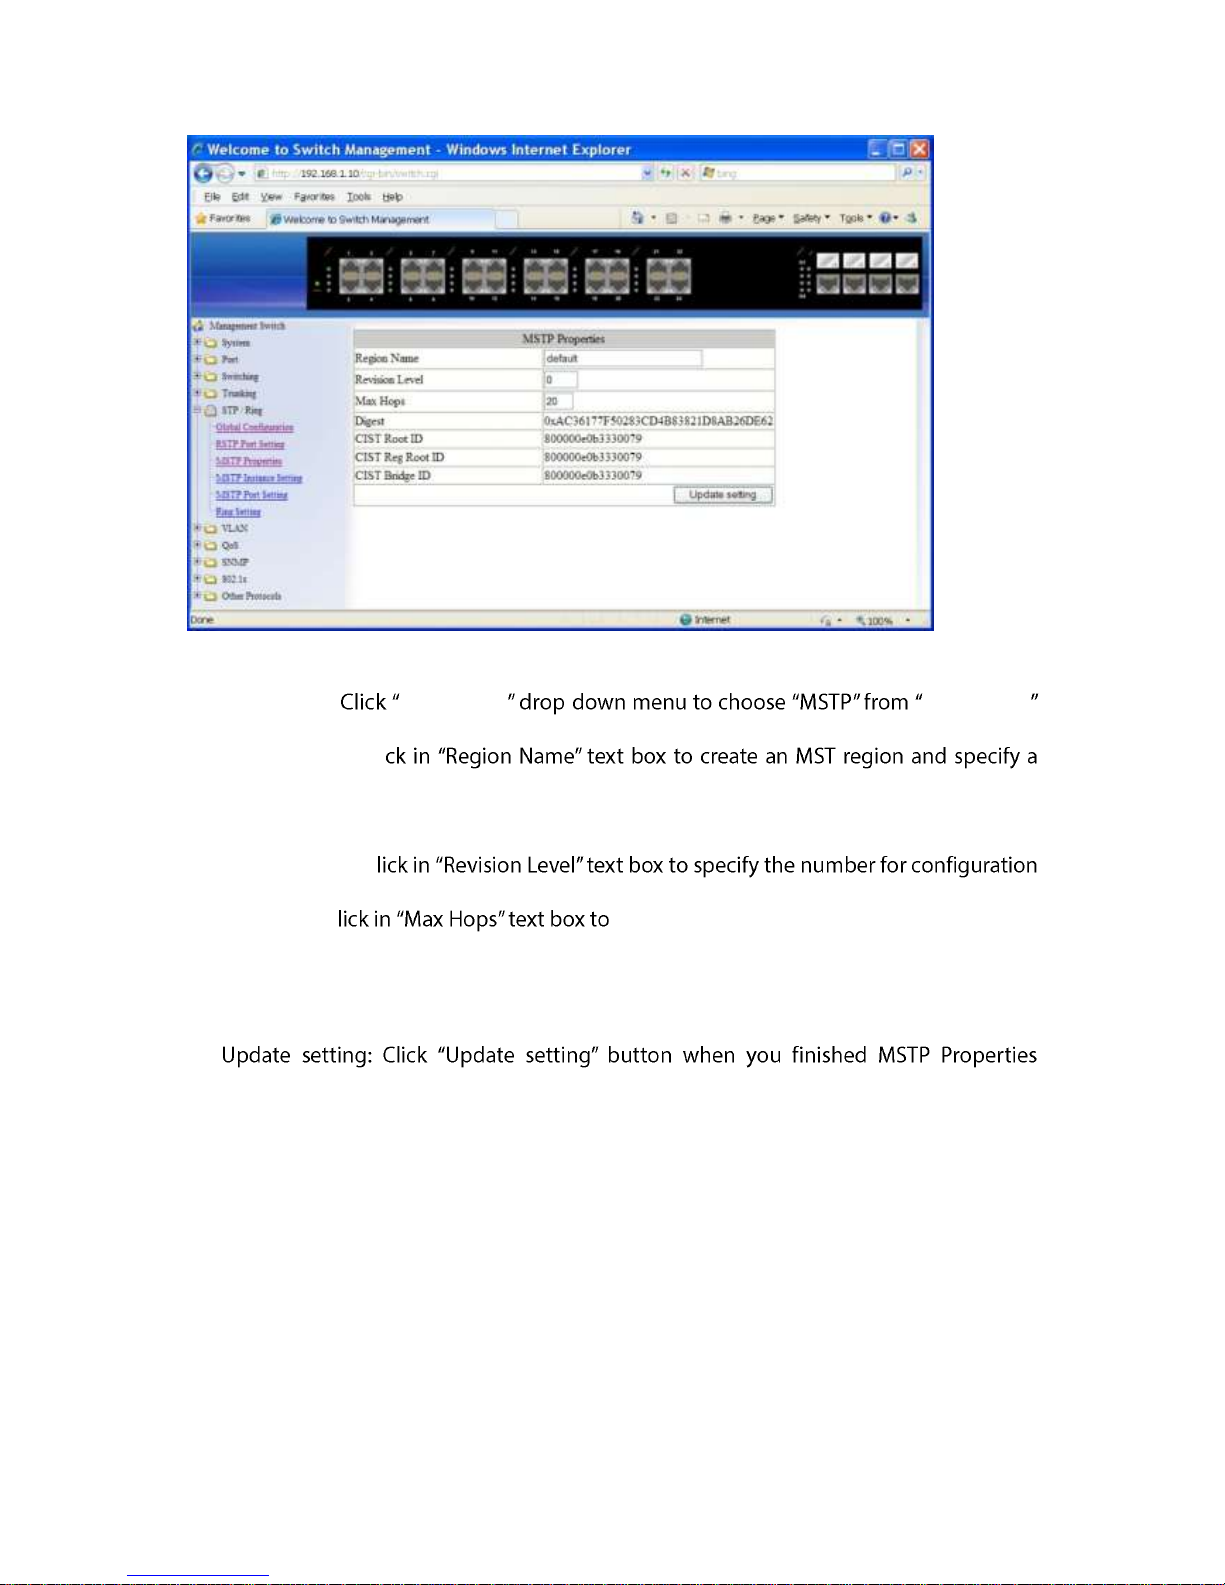
MSTP Properties
1. STP Version: STP Version - STP Version
drop-down list.
2. Region Name: Cli
name to it. MST bridges of a region form different spanning trees for different VLANs.
By default, each MST bridge starts with the region name as its bridge address. This
means each MST bridge is a region by itself, unless specifically added to one.
3. Revision Level: C
information. The default value of revision number is 0.
4. Max Hops: C specify the maximum allowed hops for BPDU
in an MST region. This parameter is used by all the instances of the MST. Specifying the
max hops for a BPDU prevents the messages from looping indefinitely in the network.
When a bridge receives a MST BPDU that has exceeded the allowed max-hops, it
discards the BPDU.
5.
setting.
Page 52
User Manual Page 52
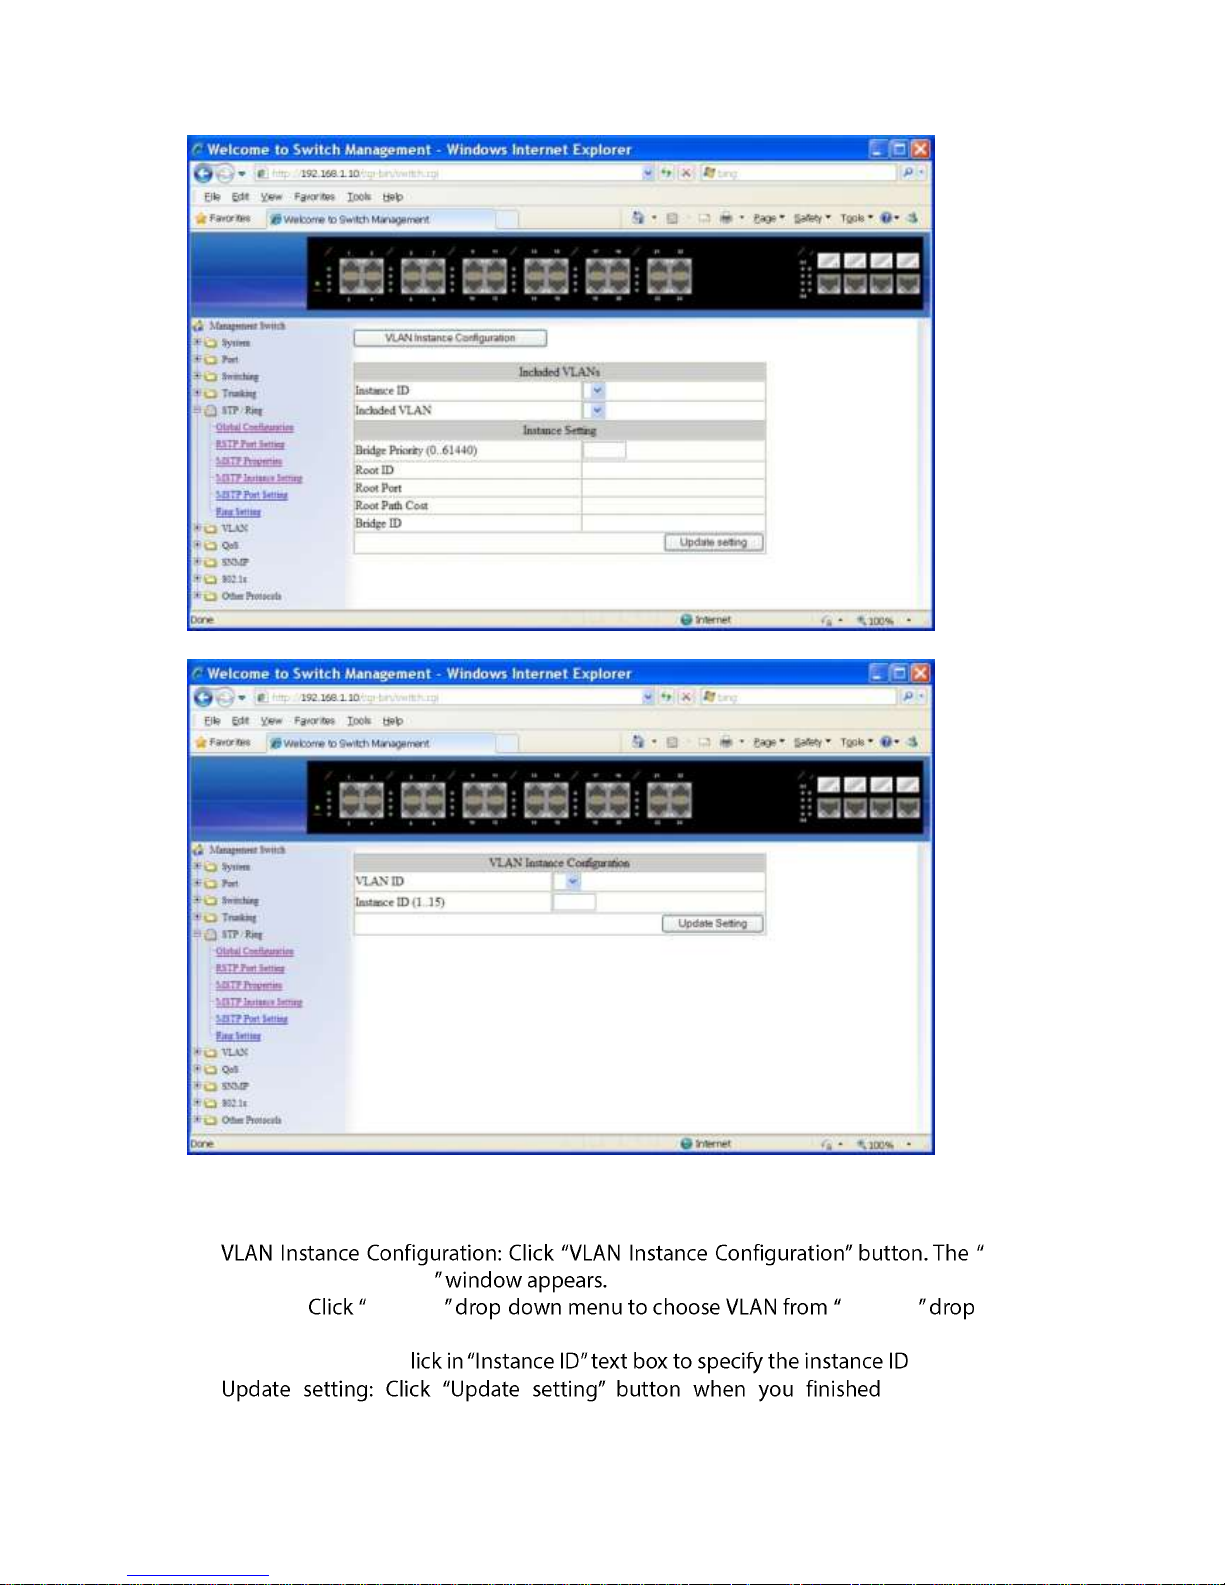
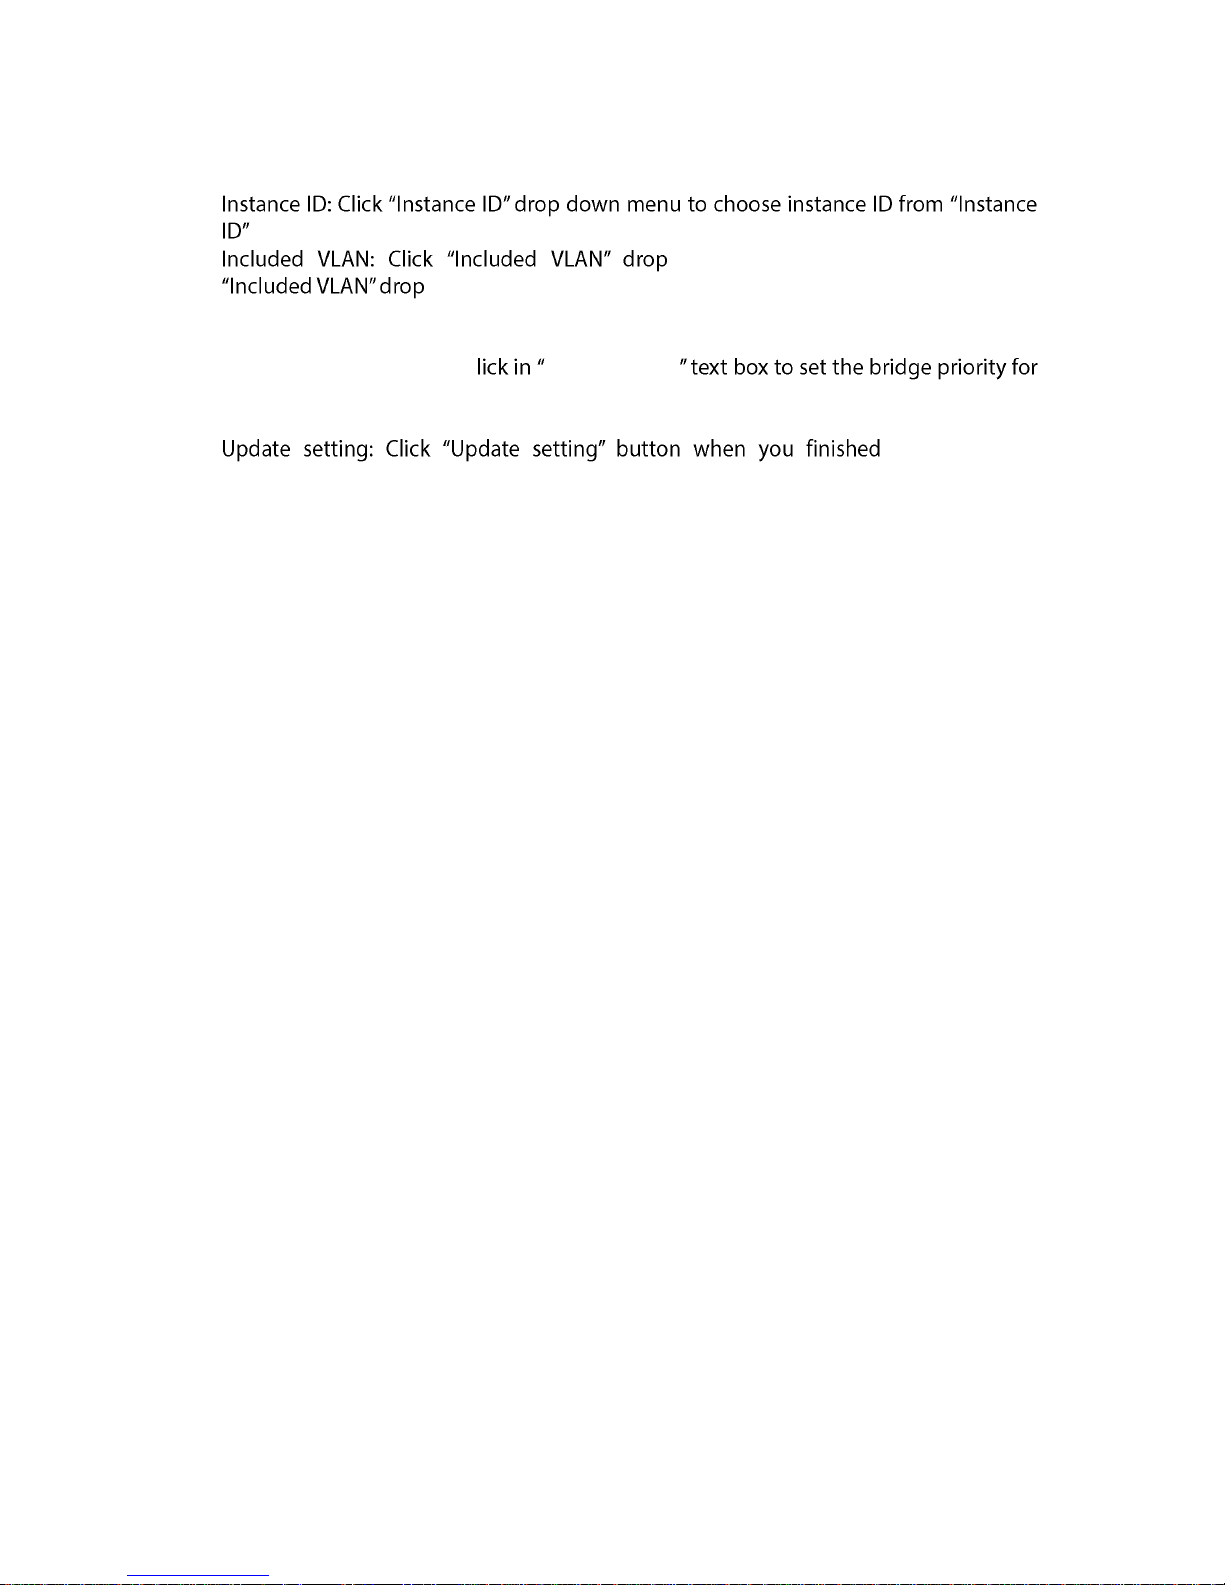
MSTP Instance Setting
VLAN Instance Configuration
1. VLAN
Instance Configuration
2. VLAN ID: VLAN ID - VLAN ID -down
list to simultaneously add multiple VLANs for the corresponding instance of a bridge.
3. Instance ID (1..15): C .
4. VLAN Instance
Configuration.
Page 53
User Manual Page 53
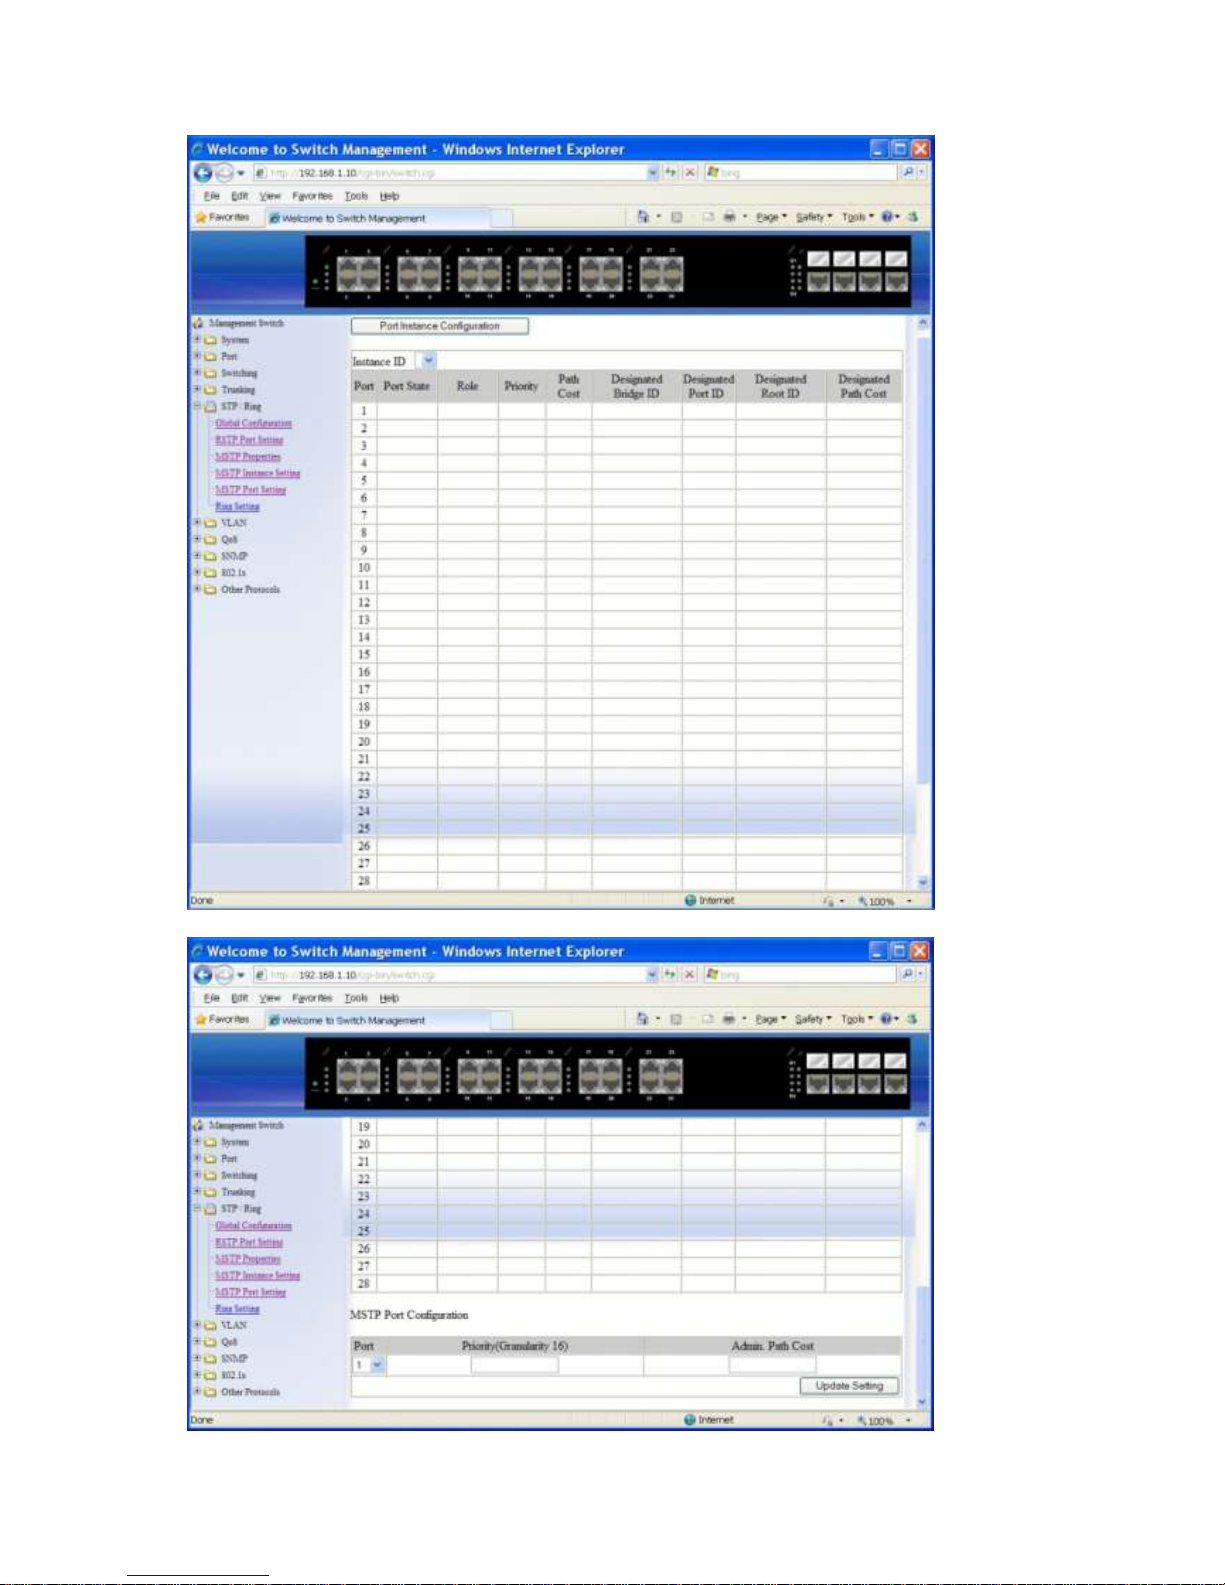
Included VLANs
1. -
drop-down list.
2. -down menu to choose VLAN from
-down list.
Instance Setting
1. Bridge Priority (0..61440): C Bridge Priority
an MST instance to the value specified. The lower the priority of the bridge, the better
the chances are the bridge becoming a root bridge or a designated bridge for the LAN.
2. VLAN Instance
Configuration.
Page 54
User Manual Page 54
Page 55
User Manual Page 55
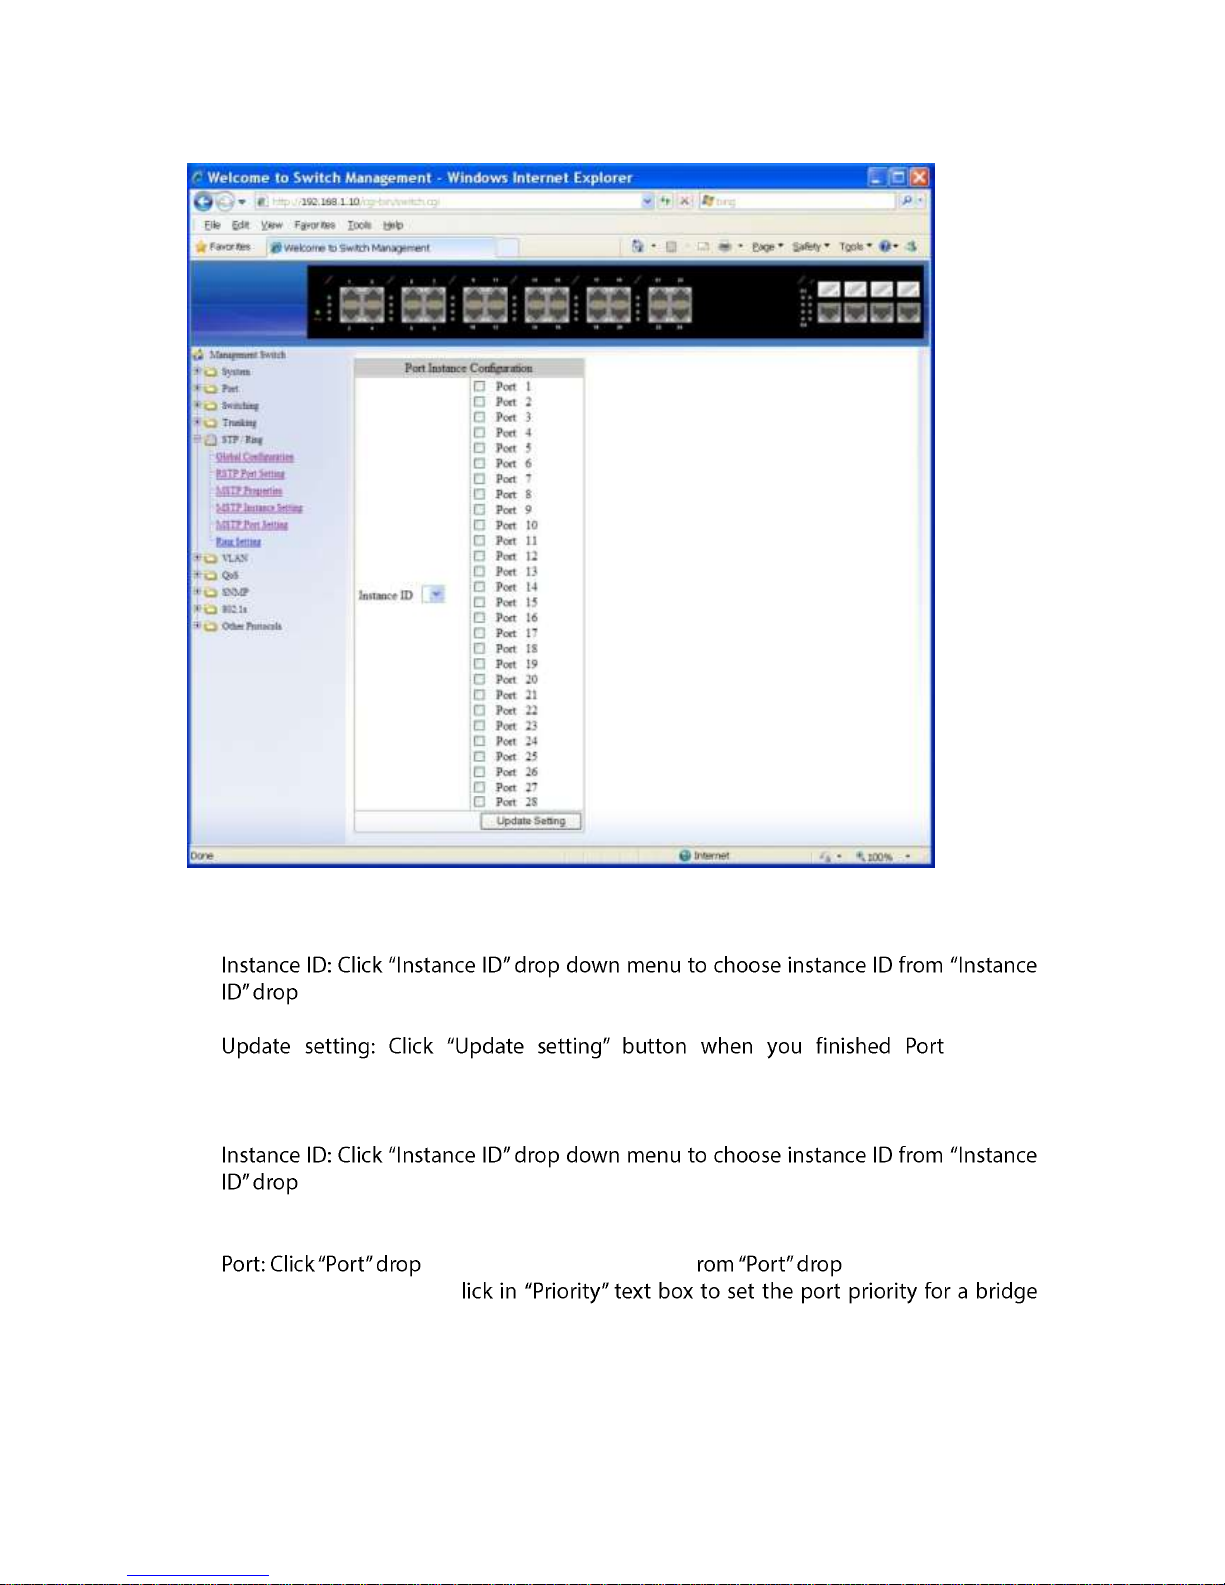
MSTP Port Setting
Port Instance Configuration
1. -
-down list.
2. Click Port 1 ~ Port 28 to assign ports to the corresponding instance ID.
3. Instance
Configuration.
Instance ID
1. -
-down list.
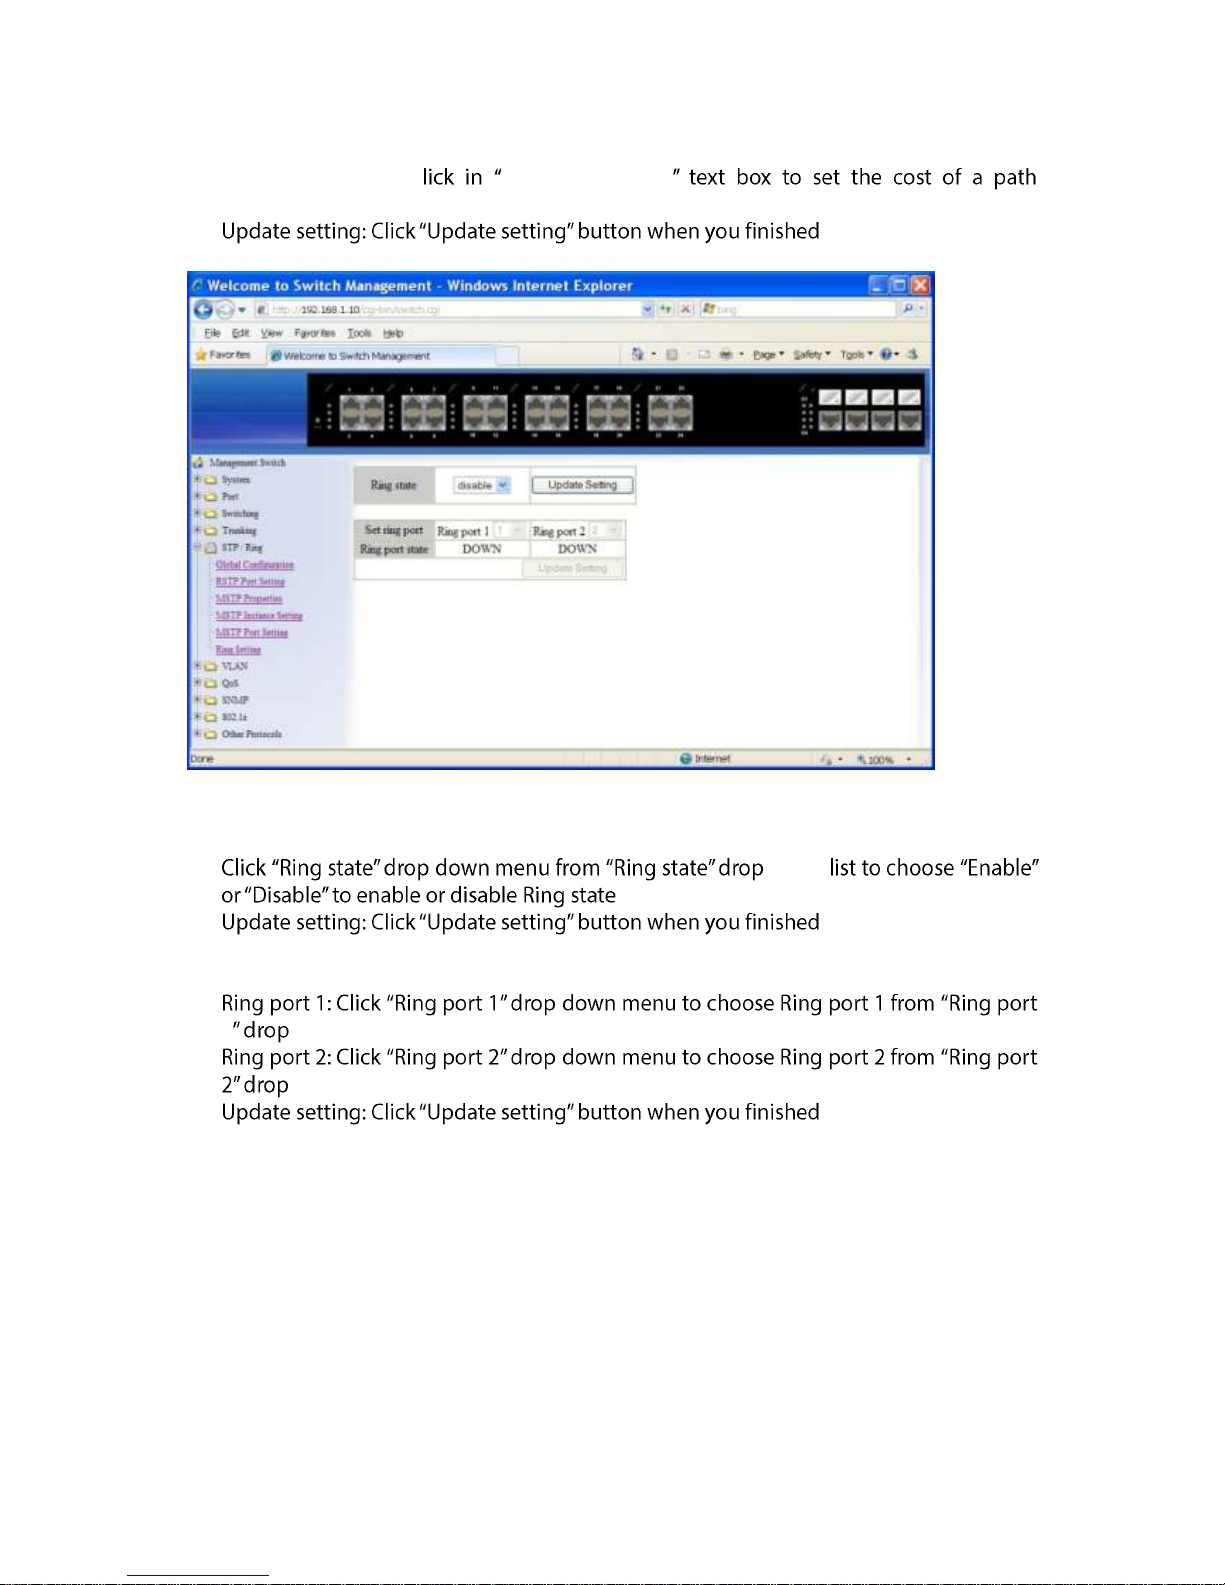
MSTP Port Configuration
1. -down menu to choose port f -down list.
2. Priority(Granularity 16): C
group. The Multiple Spanning Tree Protocol uses port priority as a tiebreaker to
determine which port should forward frames for a particular instance on a LAN, or
which port should be the root port for an instance. A lower value implies a better
priority. In the case of the same priority, the interface index will serve as the tiebreaker,
with the lower-numbered interface being preferred over others. The permitted range
Page 56
User Manual Page 56
is 0-240. The priority values can only be set in increments of 16.
3. Admin. Path Cost: C Admin. Path Cost
associated with an interface.
4. MSTP Port Setting.
Ring Setting
Ring state
1. - -down
.
2. Ring state setting.
Set ring port
1. -
1 -down list.
2. -
-down list.
3. Set ring port.
Page 57
User Manual Page 57
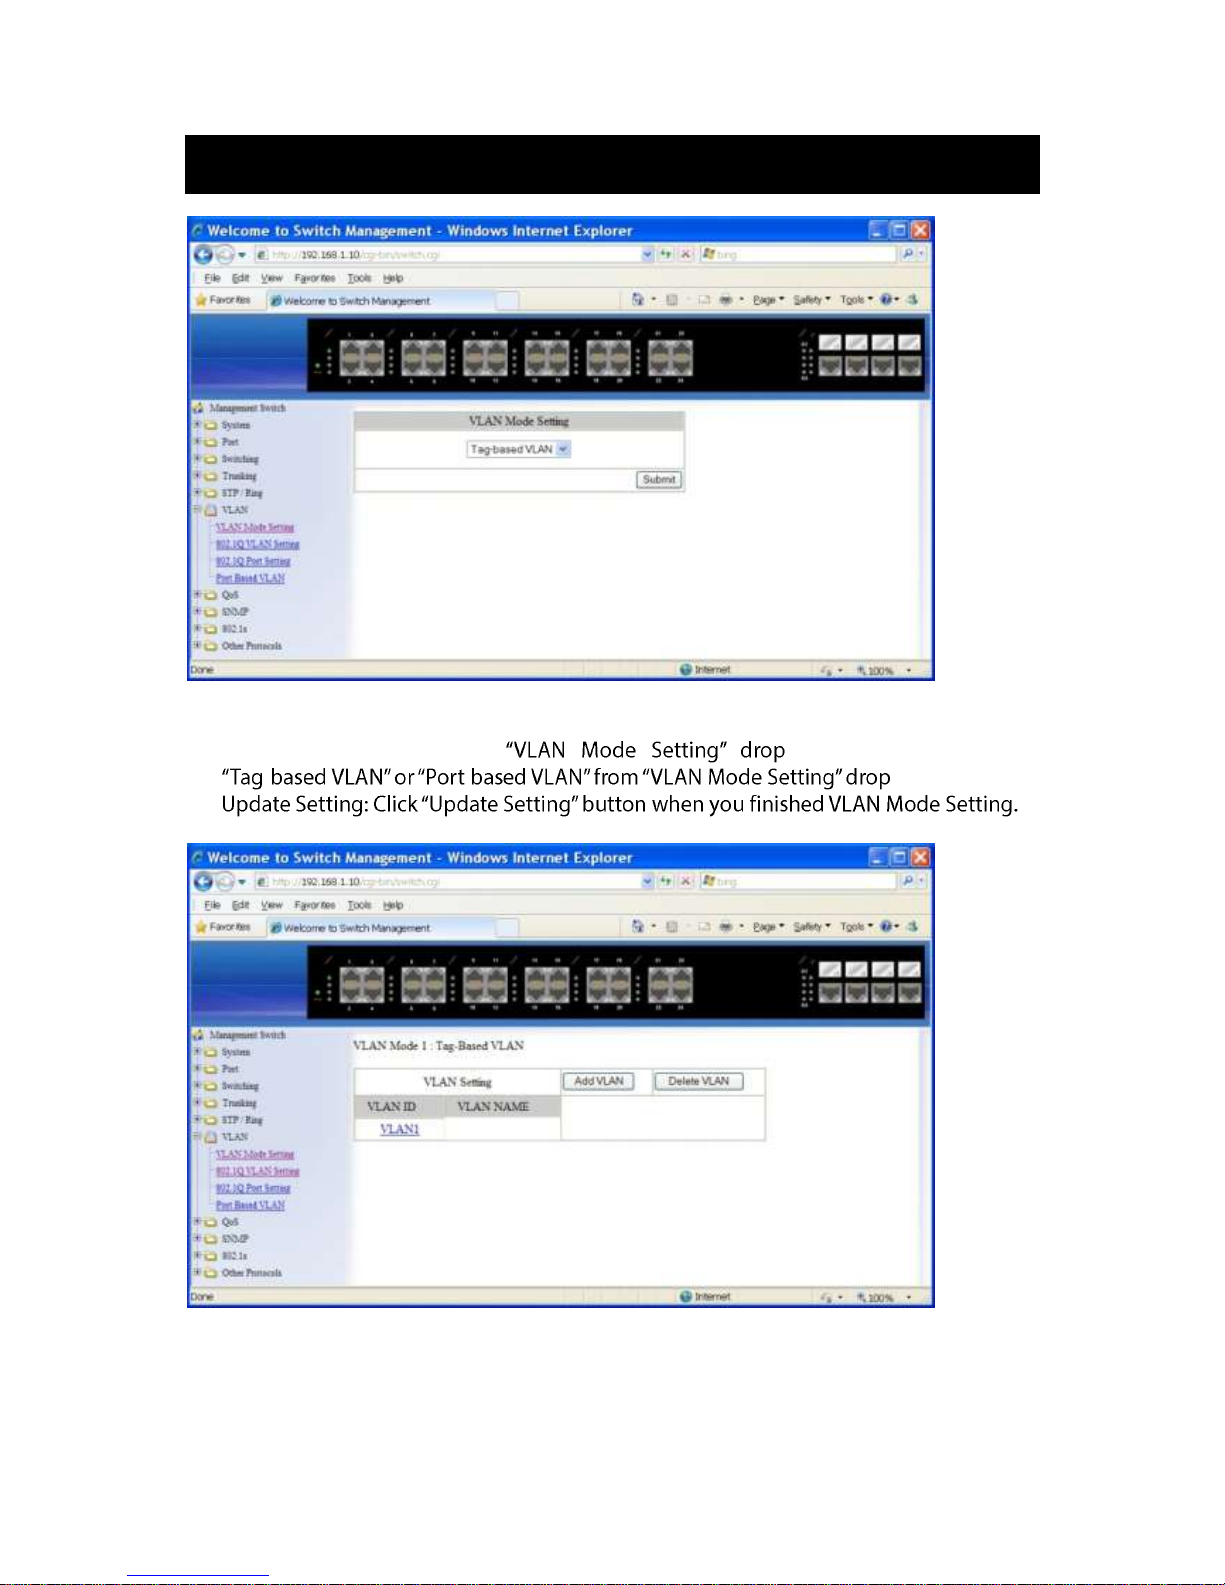
VLAN
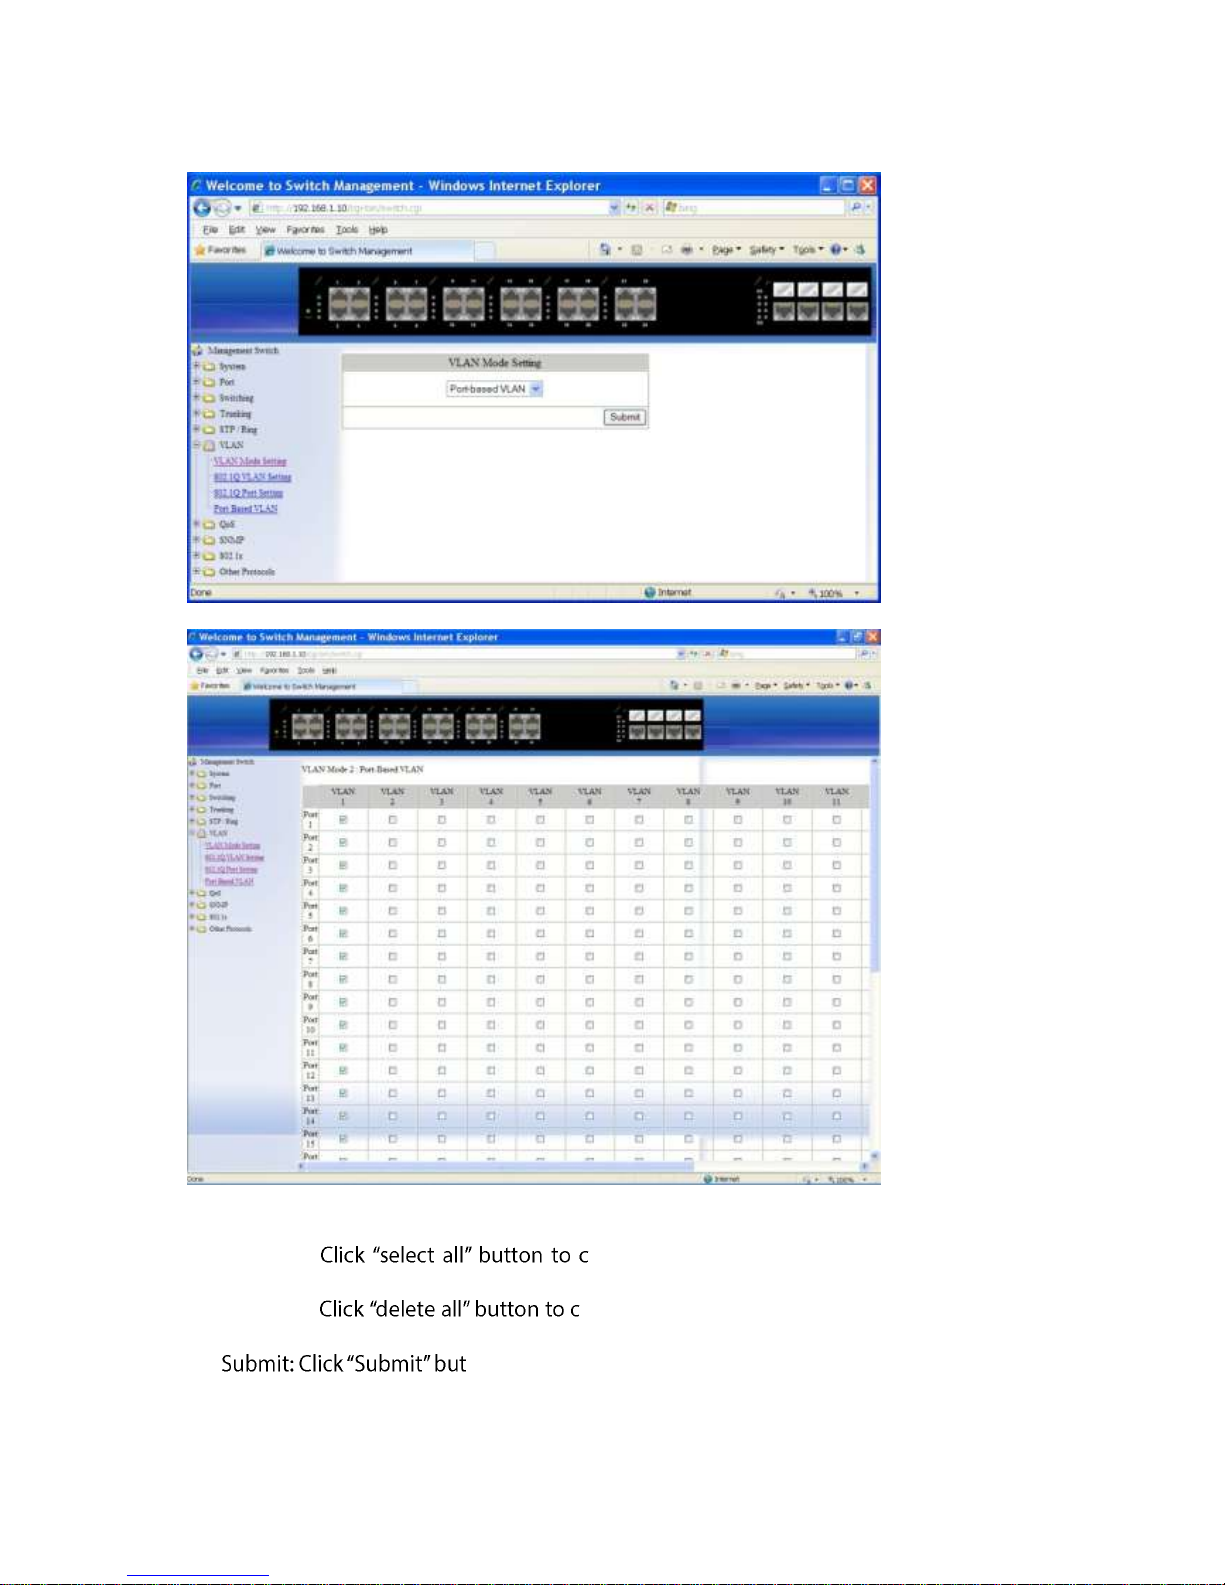
VLAN Mode Setting
1. VLAN Mode Setting: Click -down menu to Choose
- - -down list.
2.
Page 58
User Manual Page 58
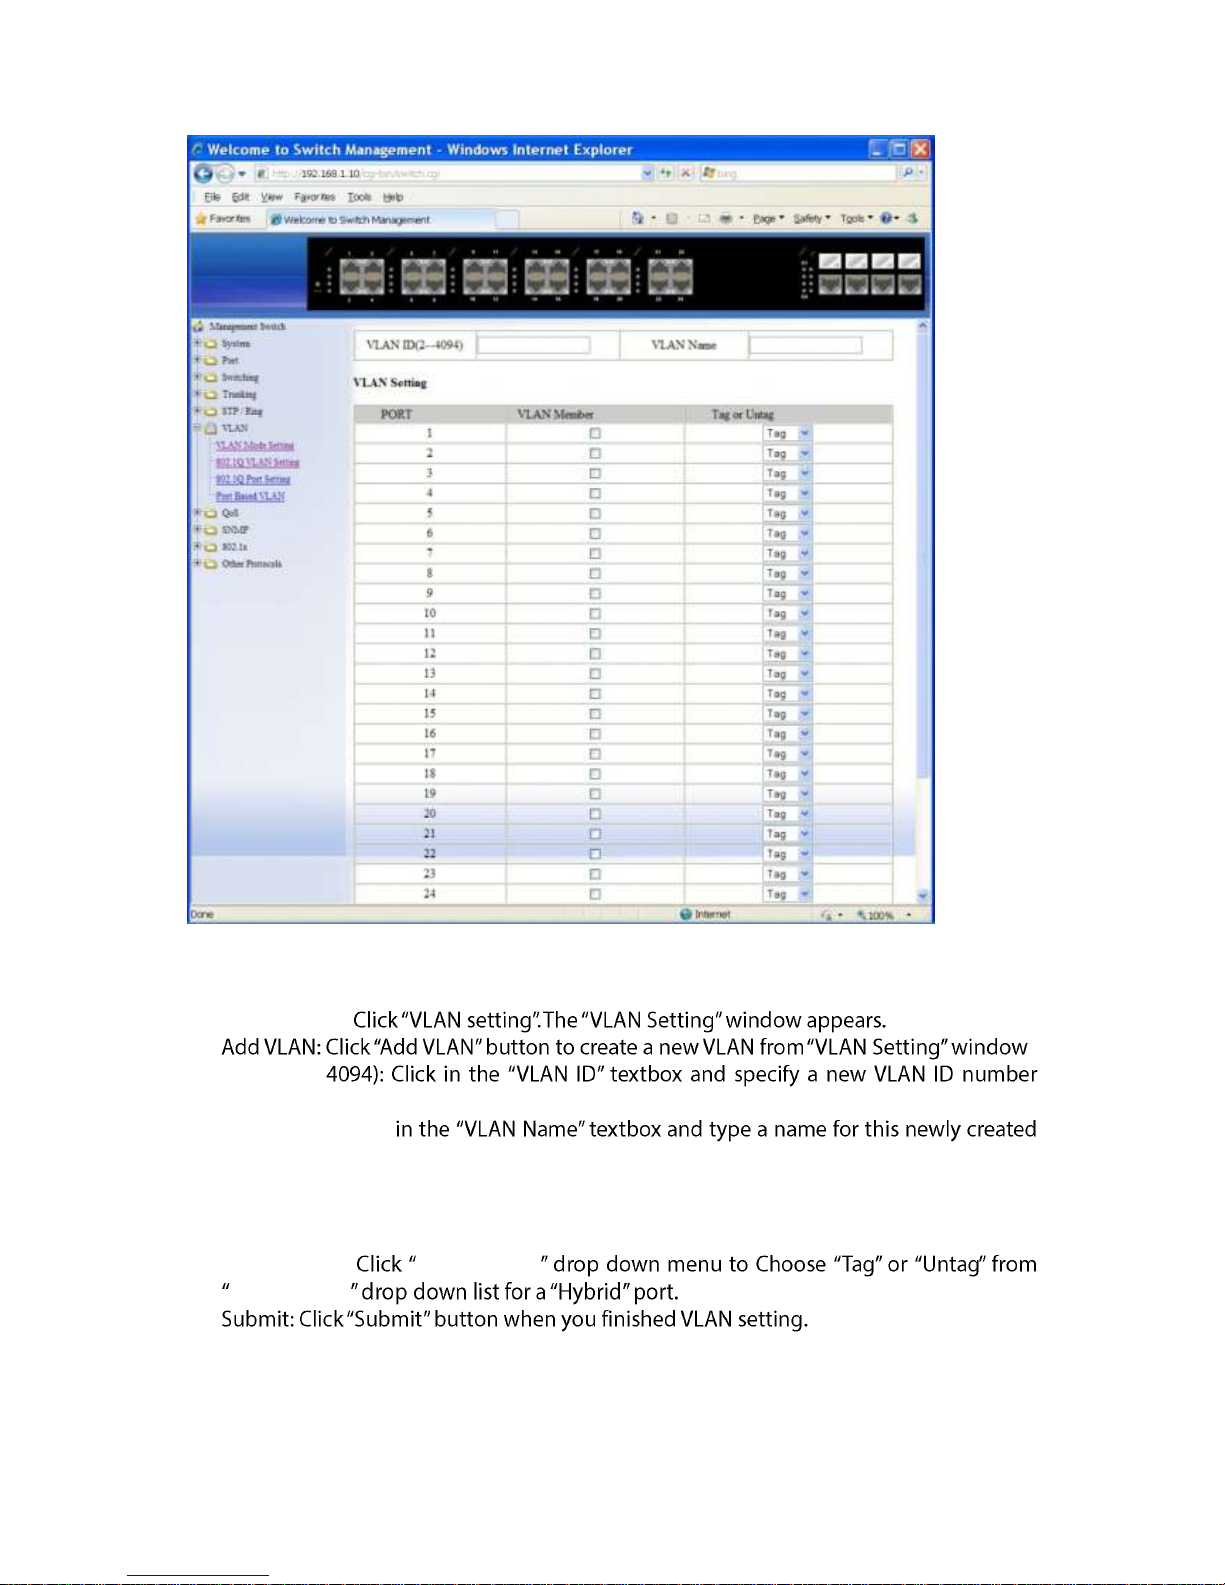
802.1Q VLAN setting
Add VLAN:
1. VLAN setting:
2. .
3. VLAN ID(2-
from 2 ~ 4094.
4. VLAN Name: Click
VLAN.
Add port to or delete port from VLAN:
1. VLAN Member: Choose the port to be added to or deleted from the VLAN.
2. Tag or Untag: Tag or Untag -
Tag or Untag -
3.
Page 59
User Manual Page 59
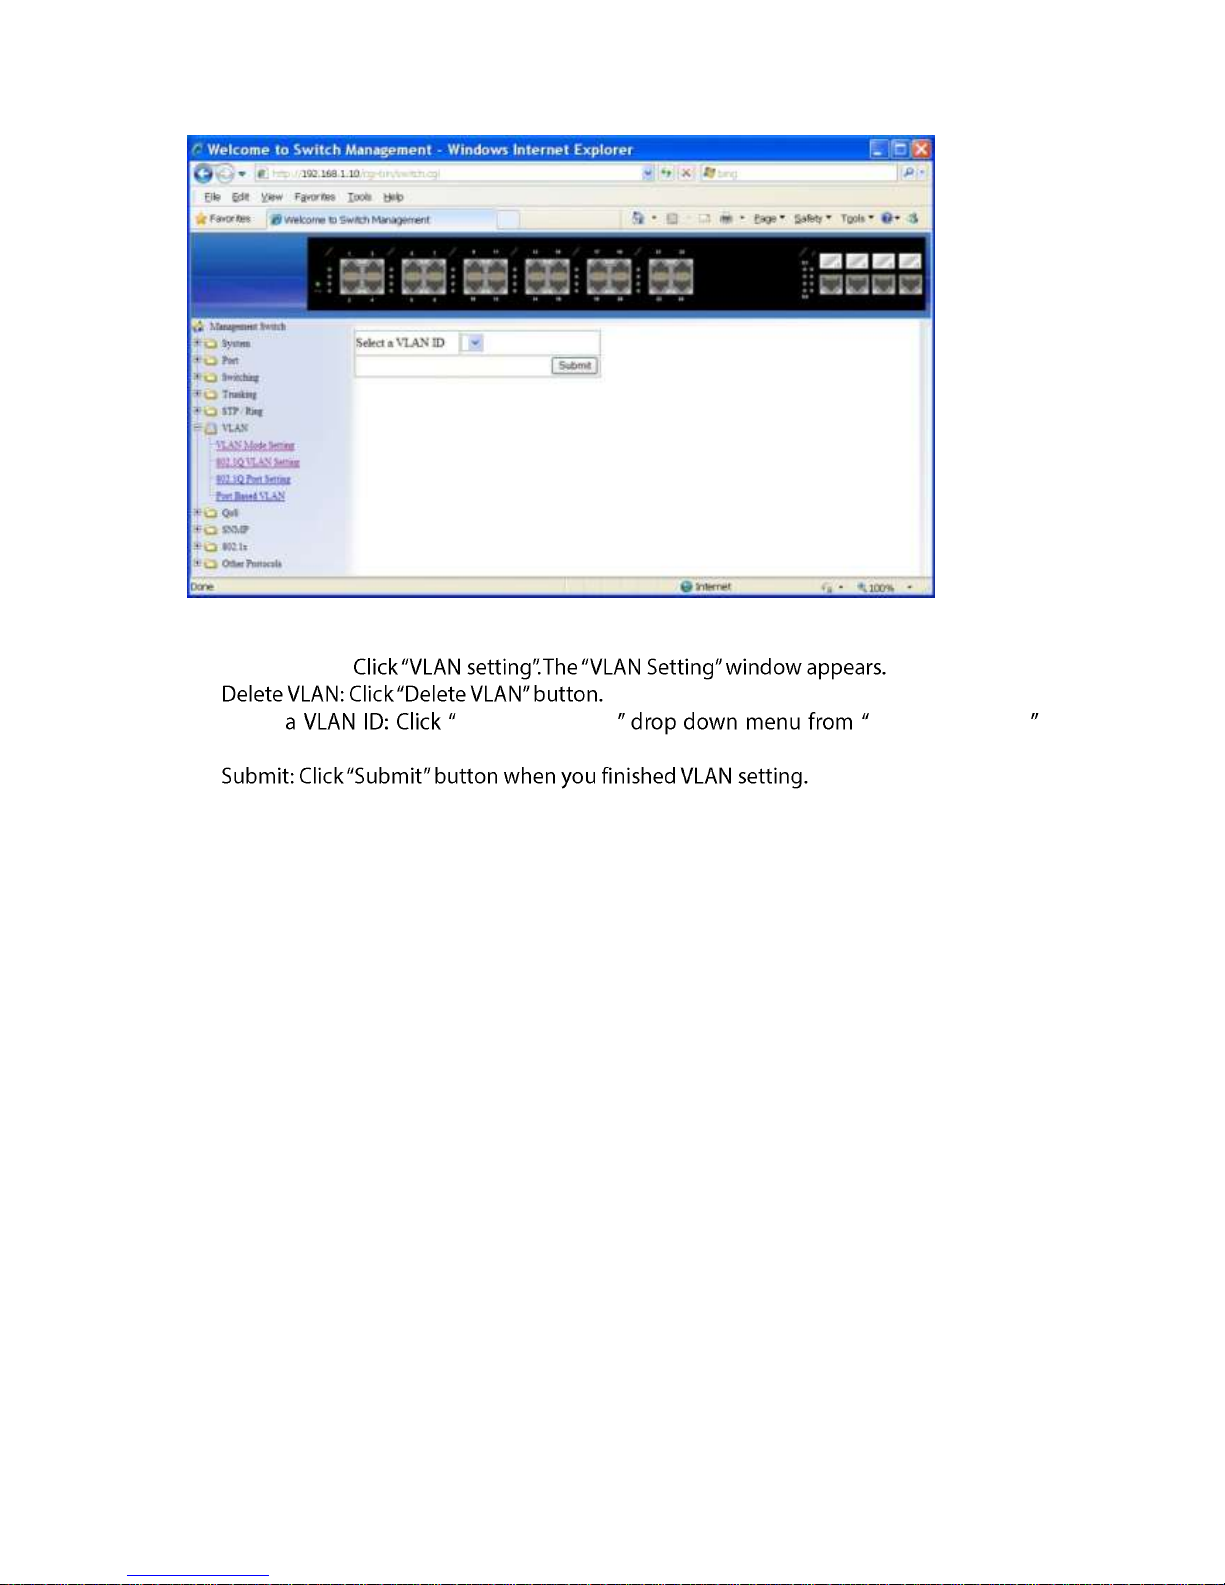
Delete VLAN:
1. VLAN setting:
2.
3. Select Select a VLAN ID - Select a VLAN ID
drop-down list to choose the VLAN to be deleted.
4.
Page 60
User Manual Page 60
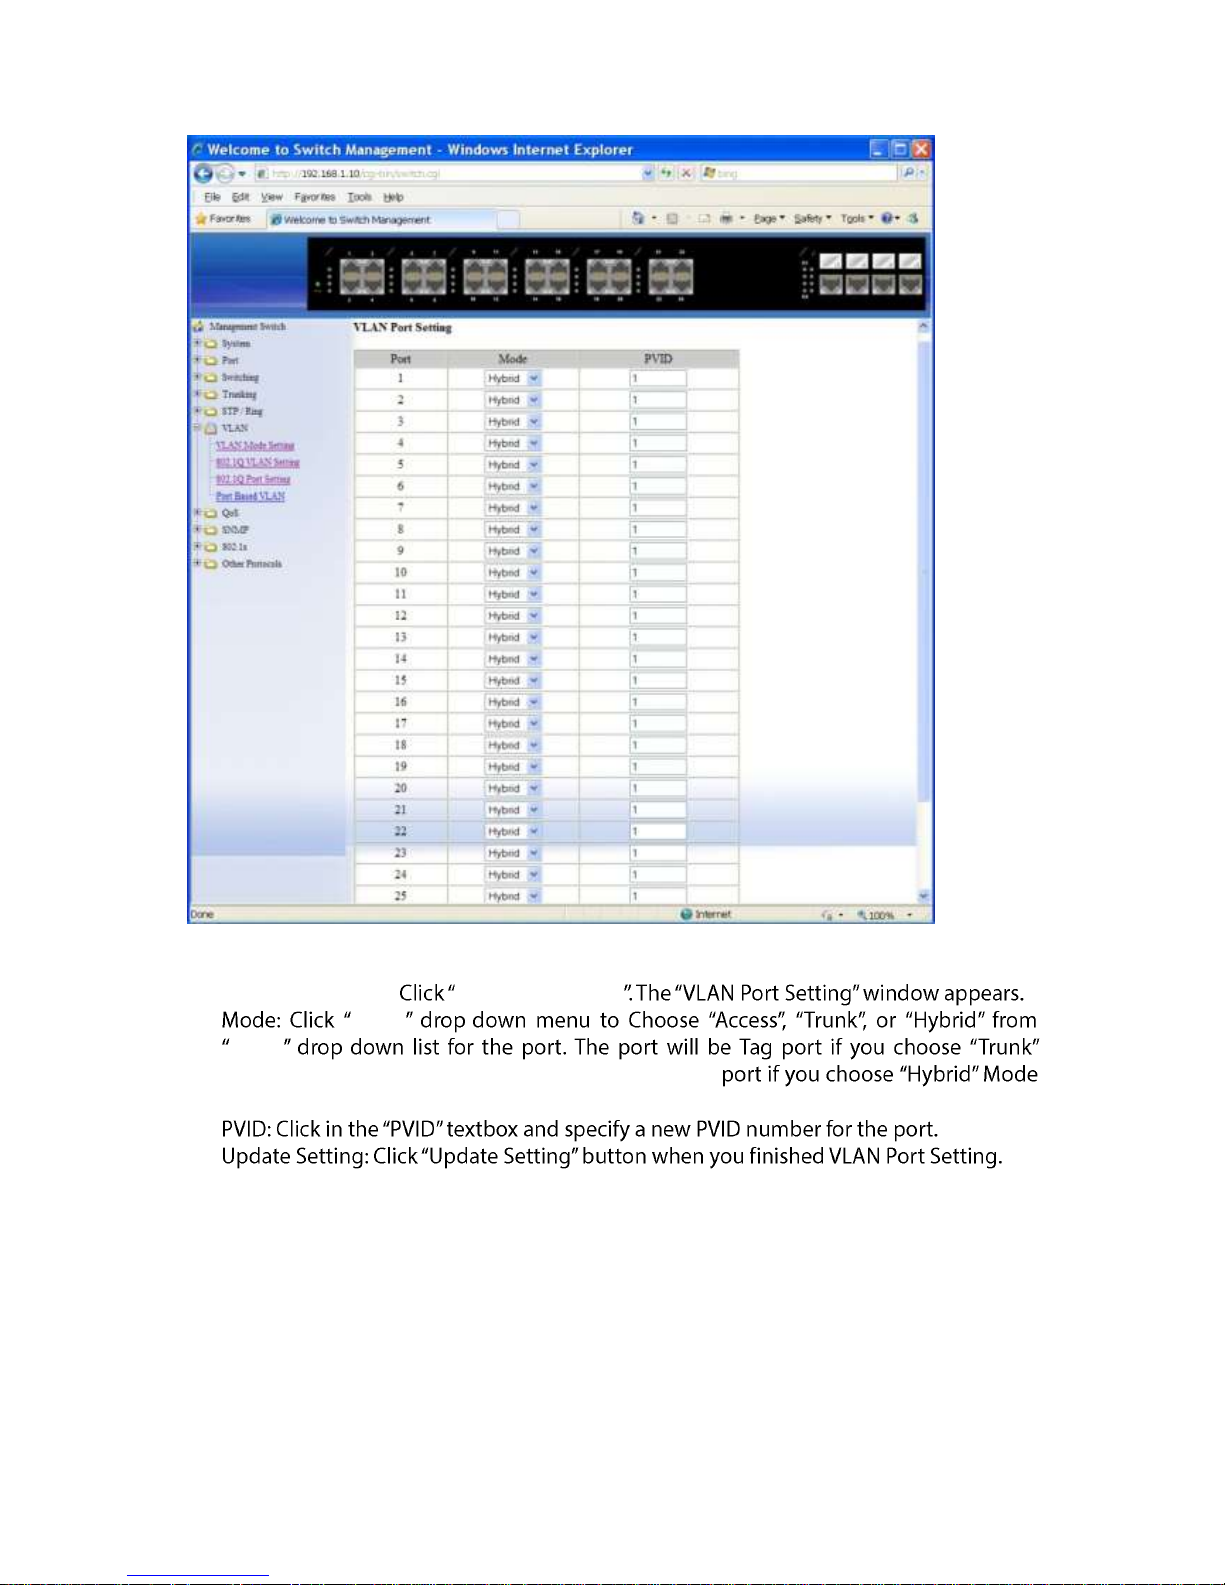
VLAN Port Setting
1. VLAN Port Setting: VLAN Port Setting
2. Mode -
Mode Mode for the port. And the port will be Tag or Untag
for the port.
3.
4.
Page 61
User Manual Page 61
Port Based VLAN
1. VLAN: Choose the port to be added to or deleted from the VLAN.
2. Select all: hoose Port 1 ~ Port 28 all to be added to the
VLAN.
3. Delete all: hoose Port 1 ~ Port 28 all to be deleted from the
VLAN.
4. ton when you finished Port Based VLAN setting.
Page 62
User Manual Page 62
QoS
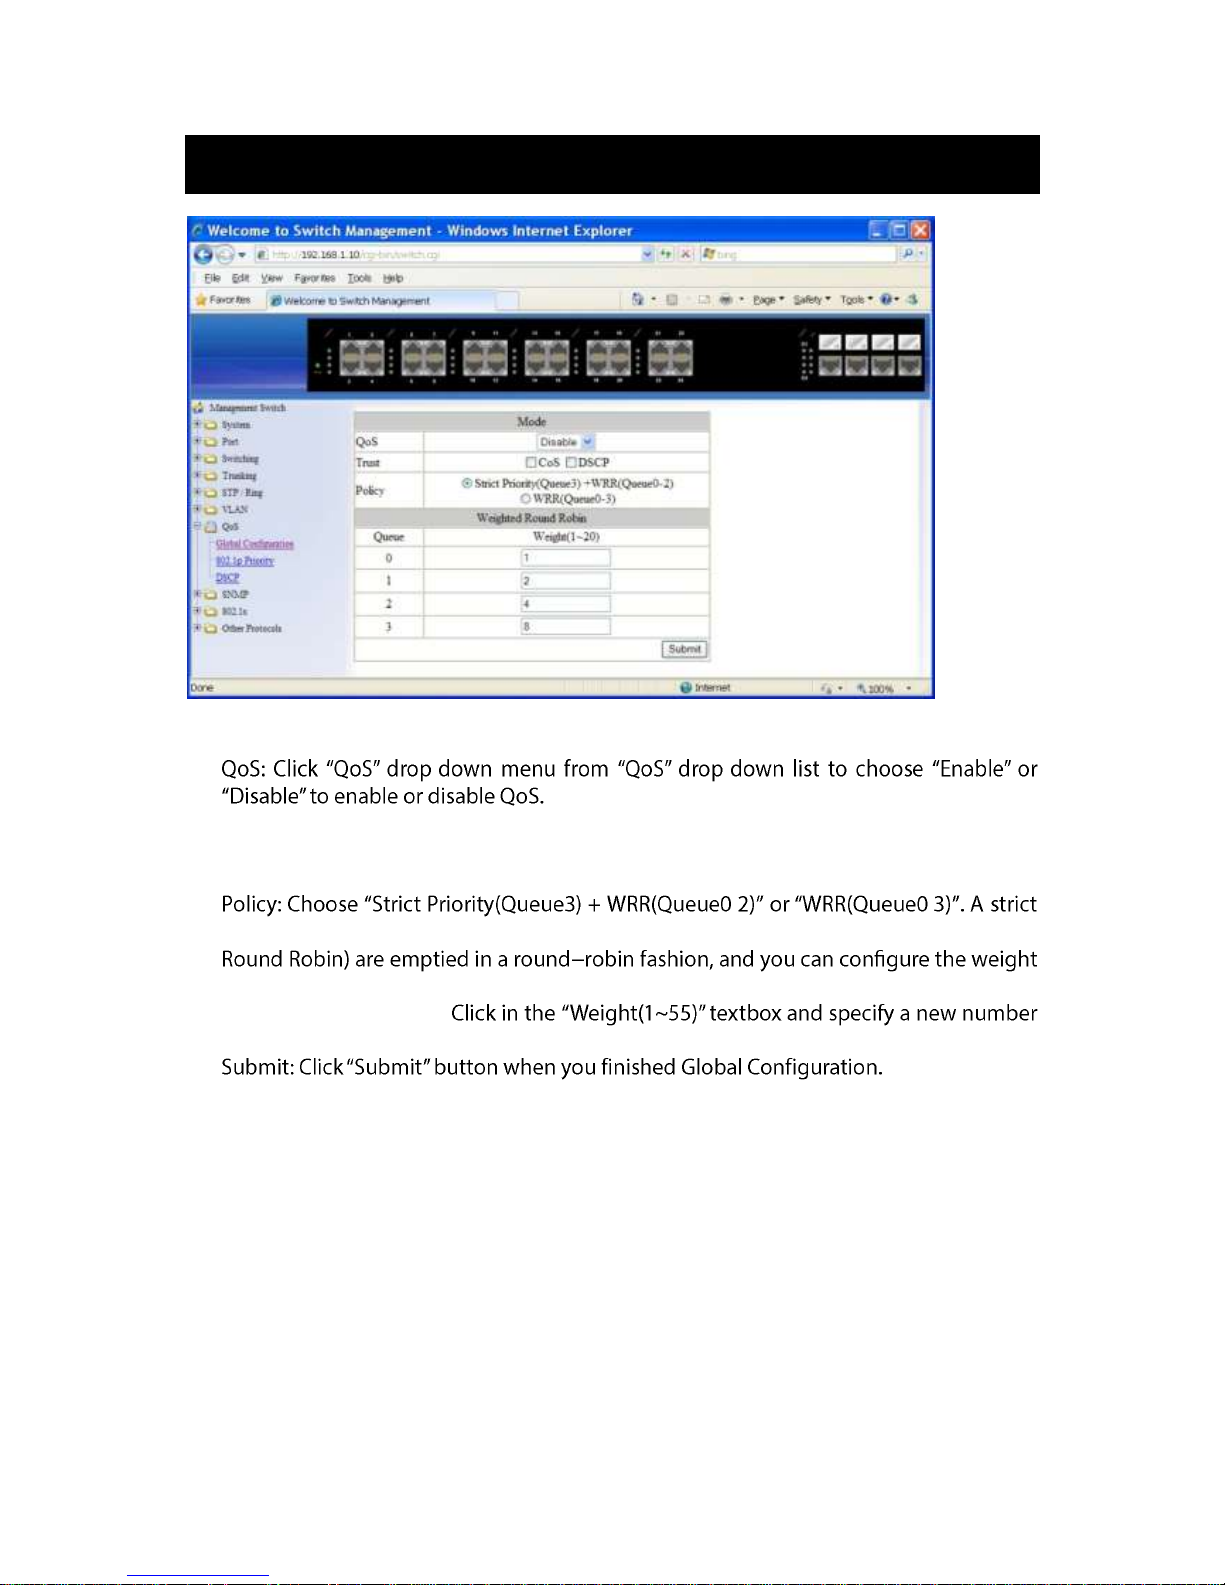
Global Configuration
1. - -
2. Trust: Enable or disable the switch port to trust the CoS (Class of Service) labels of all
traffic received on that port. Enable or disable a routed port to trust the DSCP
(Differentiated Service Code Point) labels of all traffic received on that port.
3. - priority queue is always emptied first. The queues that are used in the WRR (Weighted
for each queue.
4. Weighted Round Robin:
from 1 ~ 55 for Queue 0 ~ 3.
5.
Page 63
User Manual Page 63
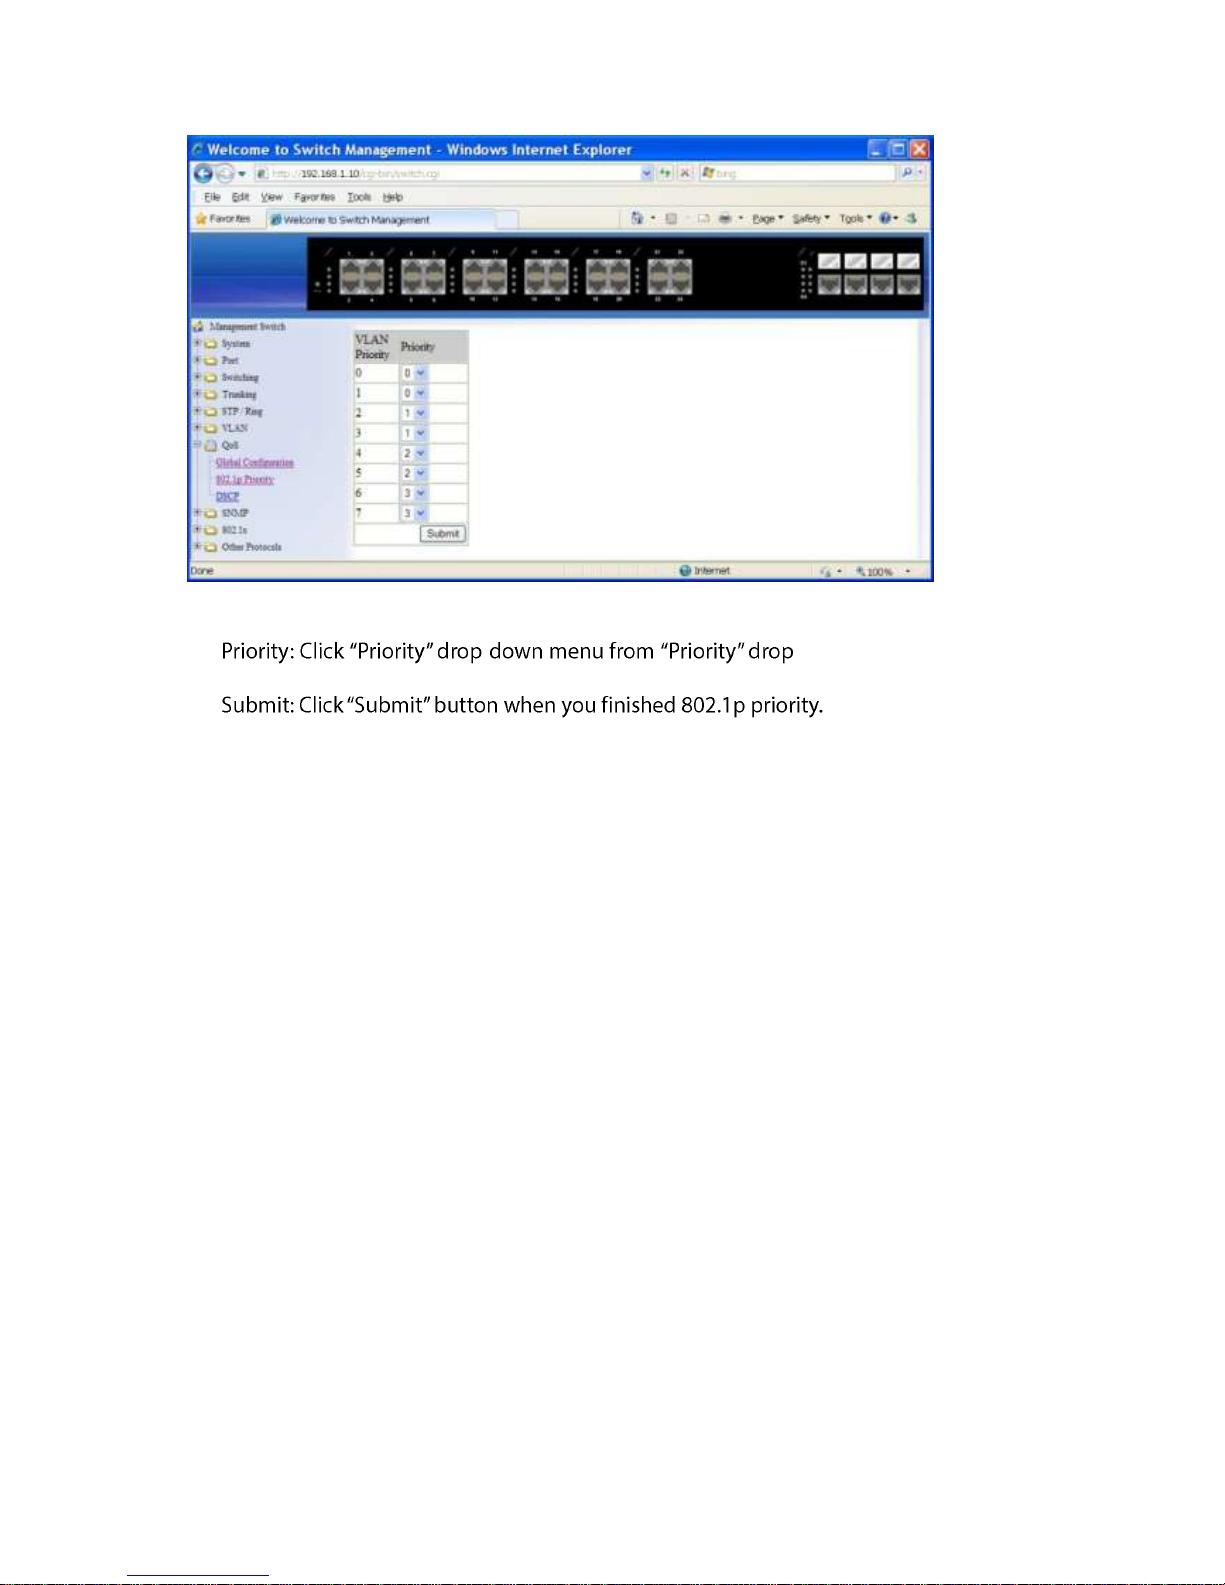
802.1p Priority
1. - -down list to choose 0 ~ 3
for VLAN Priority 0 ~ 7.
2.
Page 64
User Manual Page 64
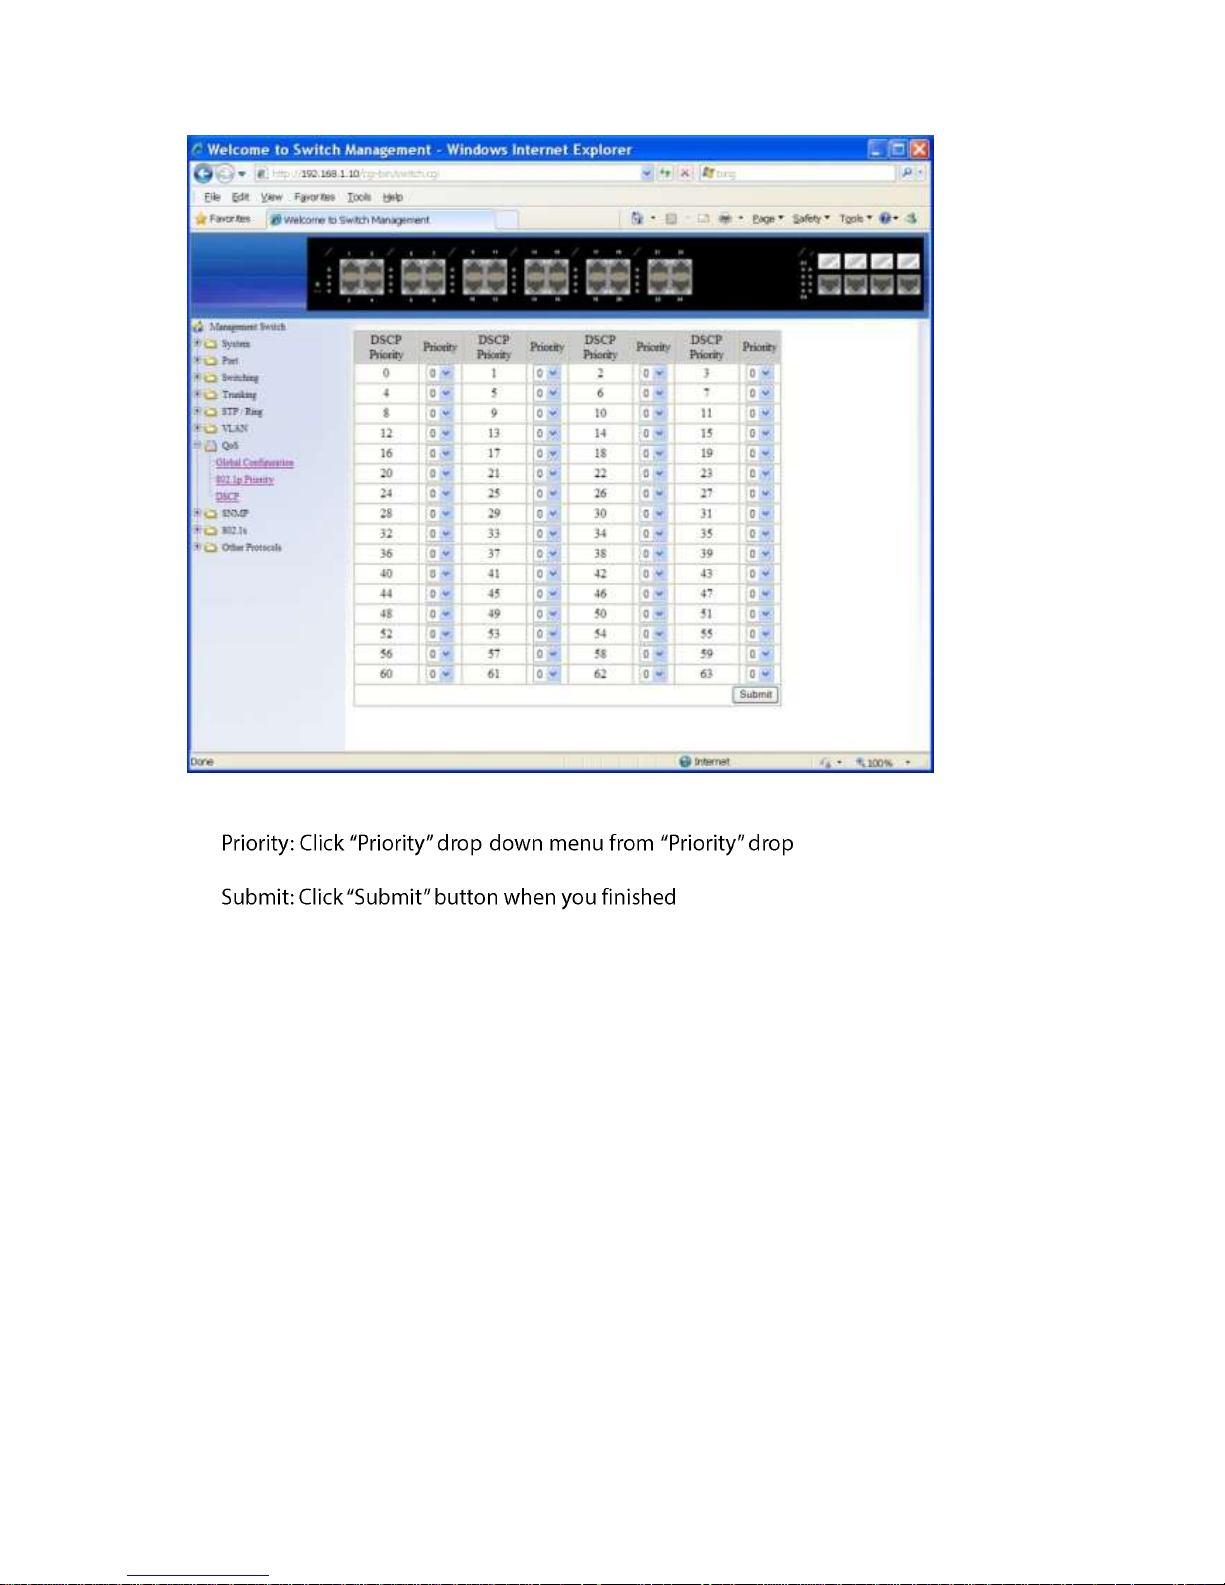
DSCP
1. - -down list to choose 0 ~ 3
for DSCP Priority 0 ~ 63.
2. DSCP.
Page 65
User Manual Page 65
SNMP
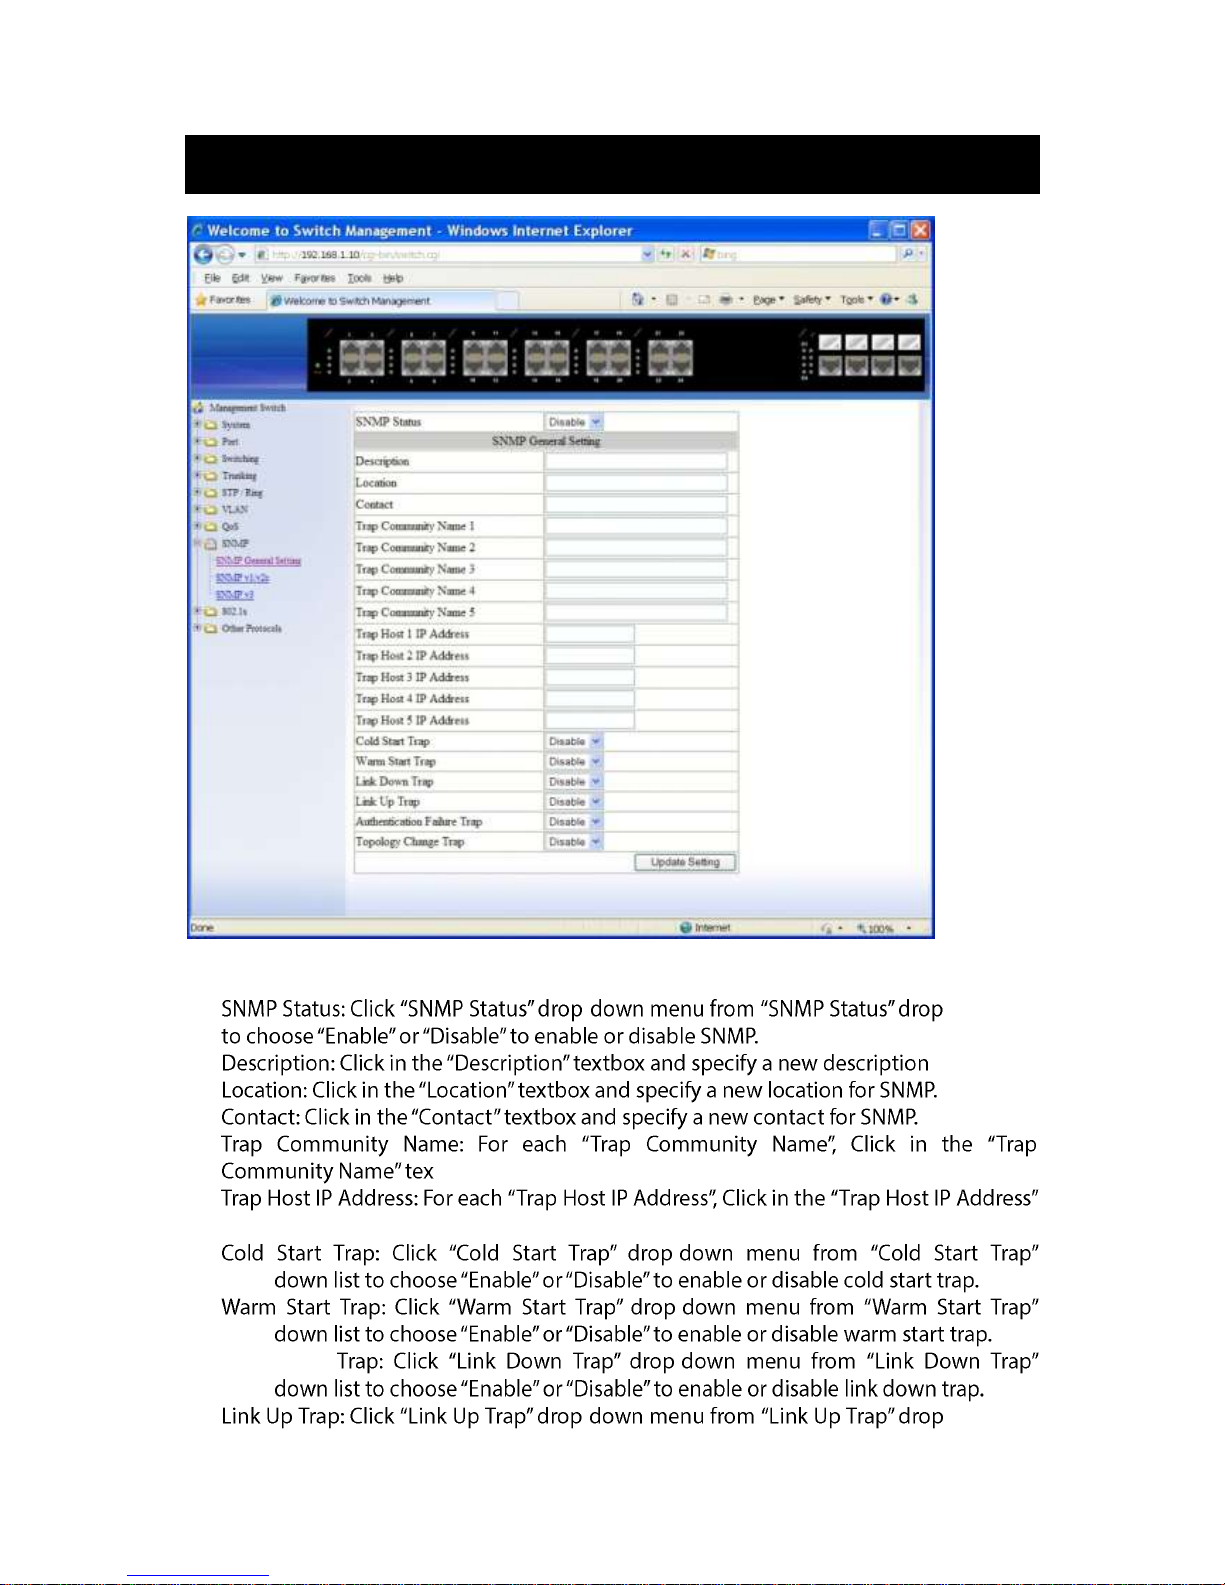
SNMP General Setting
1. - -down list
2. for SNMP.
3.
4.
5.
tbox and specify a trap community name.
6.
textbox and specify a trap host IP address.
7. drop-
8. drop-
9. Link Down -
drop-
10. - -down list
Page 66
User Manual Page 66
11. -down menu from
-
disable authentication failure trap.
12. -
-
topology change trap.
13. General
Setting.
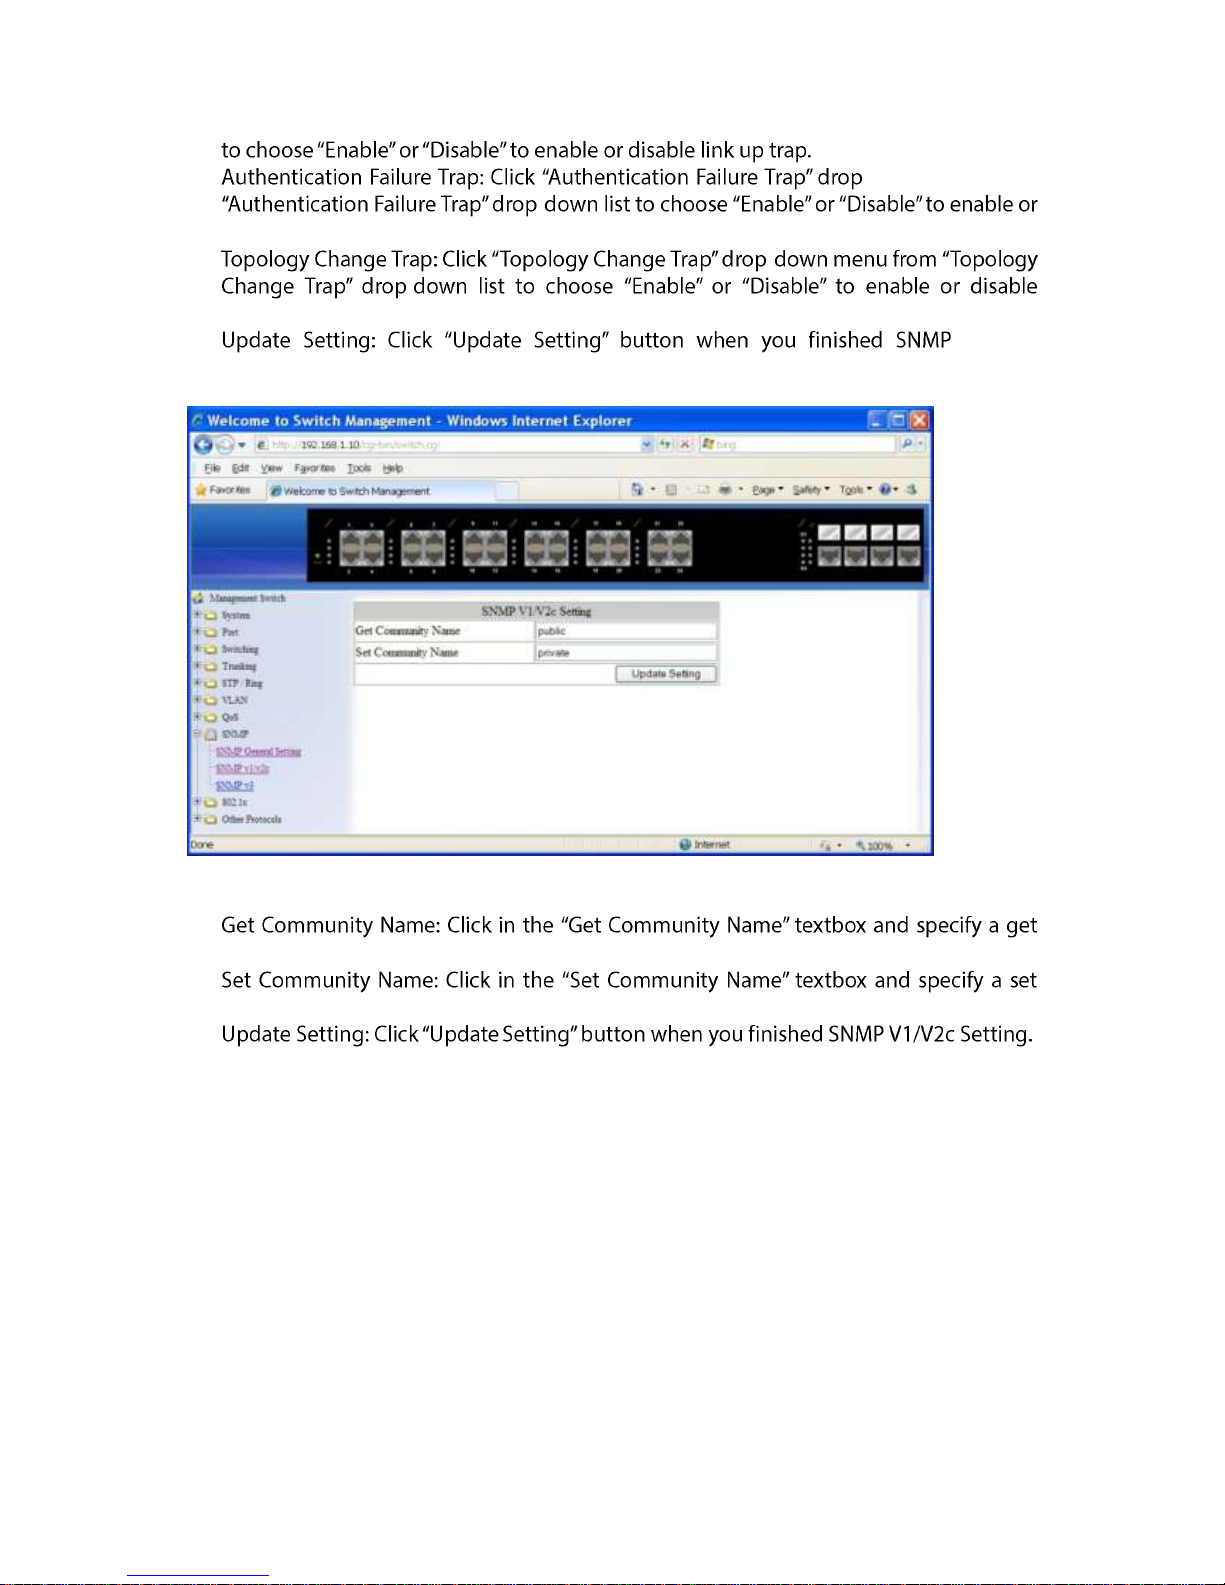
SNMP v1/v2c
1.
community name.
2.
community name.
3.
Page 67
User Manual Page 67
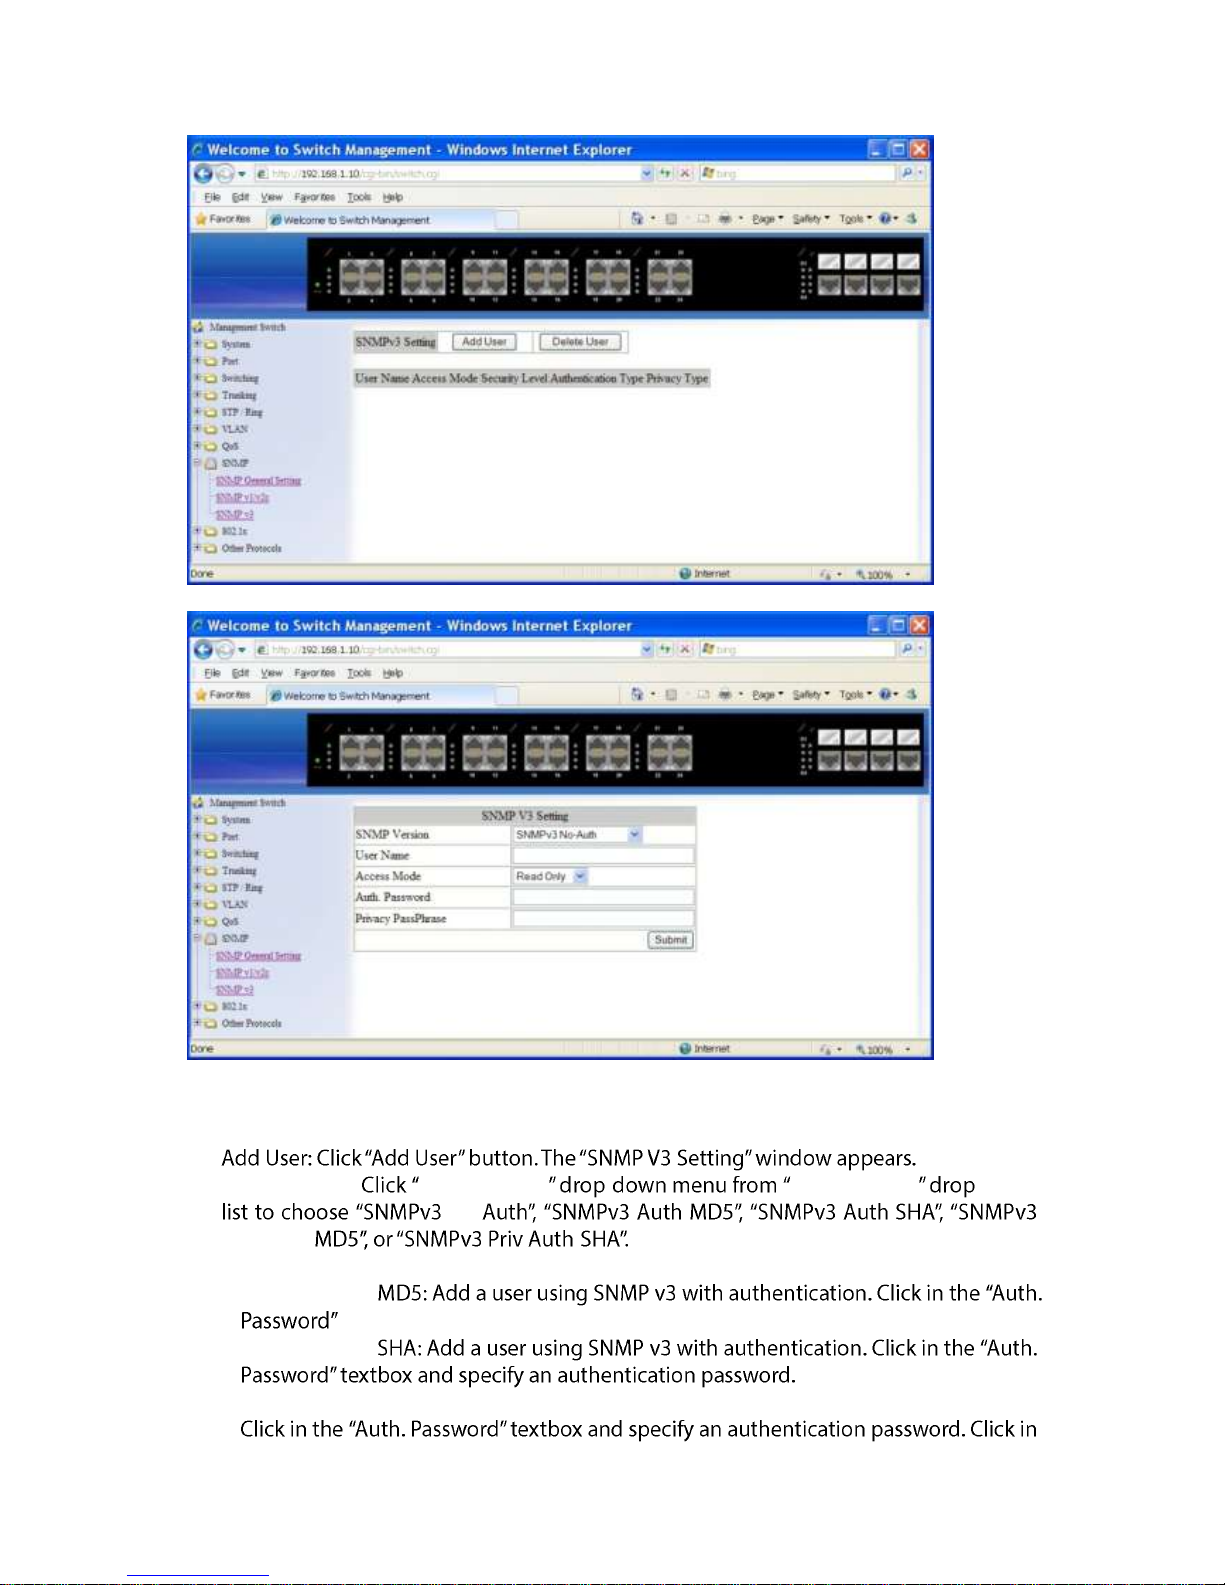
SNMP v3
Add User:
1.
2. SNMP Version: SNMP Version - SNMP Version -down
No- - -
Priv Auth- -
SNMPv3 No-Auth: Add a user using SNMP v3 without authentication.
SNMPv3 Auth-
textbox and specify an authentication password.
SNMPv3 Auth-
SNMPv3 Priv Auth-MD5: Add a user using SNMP v3 with authentication and privacy.
Page 68
User Manual Page 68
SNMPv3 Priv Auth-SHA: Add a user using SNMP v3 with authentication and privacy.
Click i
3.
SNMP v3.
4. Access Mode: Cli - -down list
Read Only: Add a user using SNMP v3 with read-only access mode.
Read/Write: Add an user using SNMP v3 with read-write access mode
5. Submit Submit
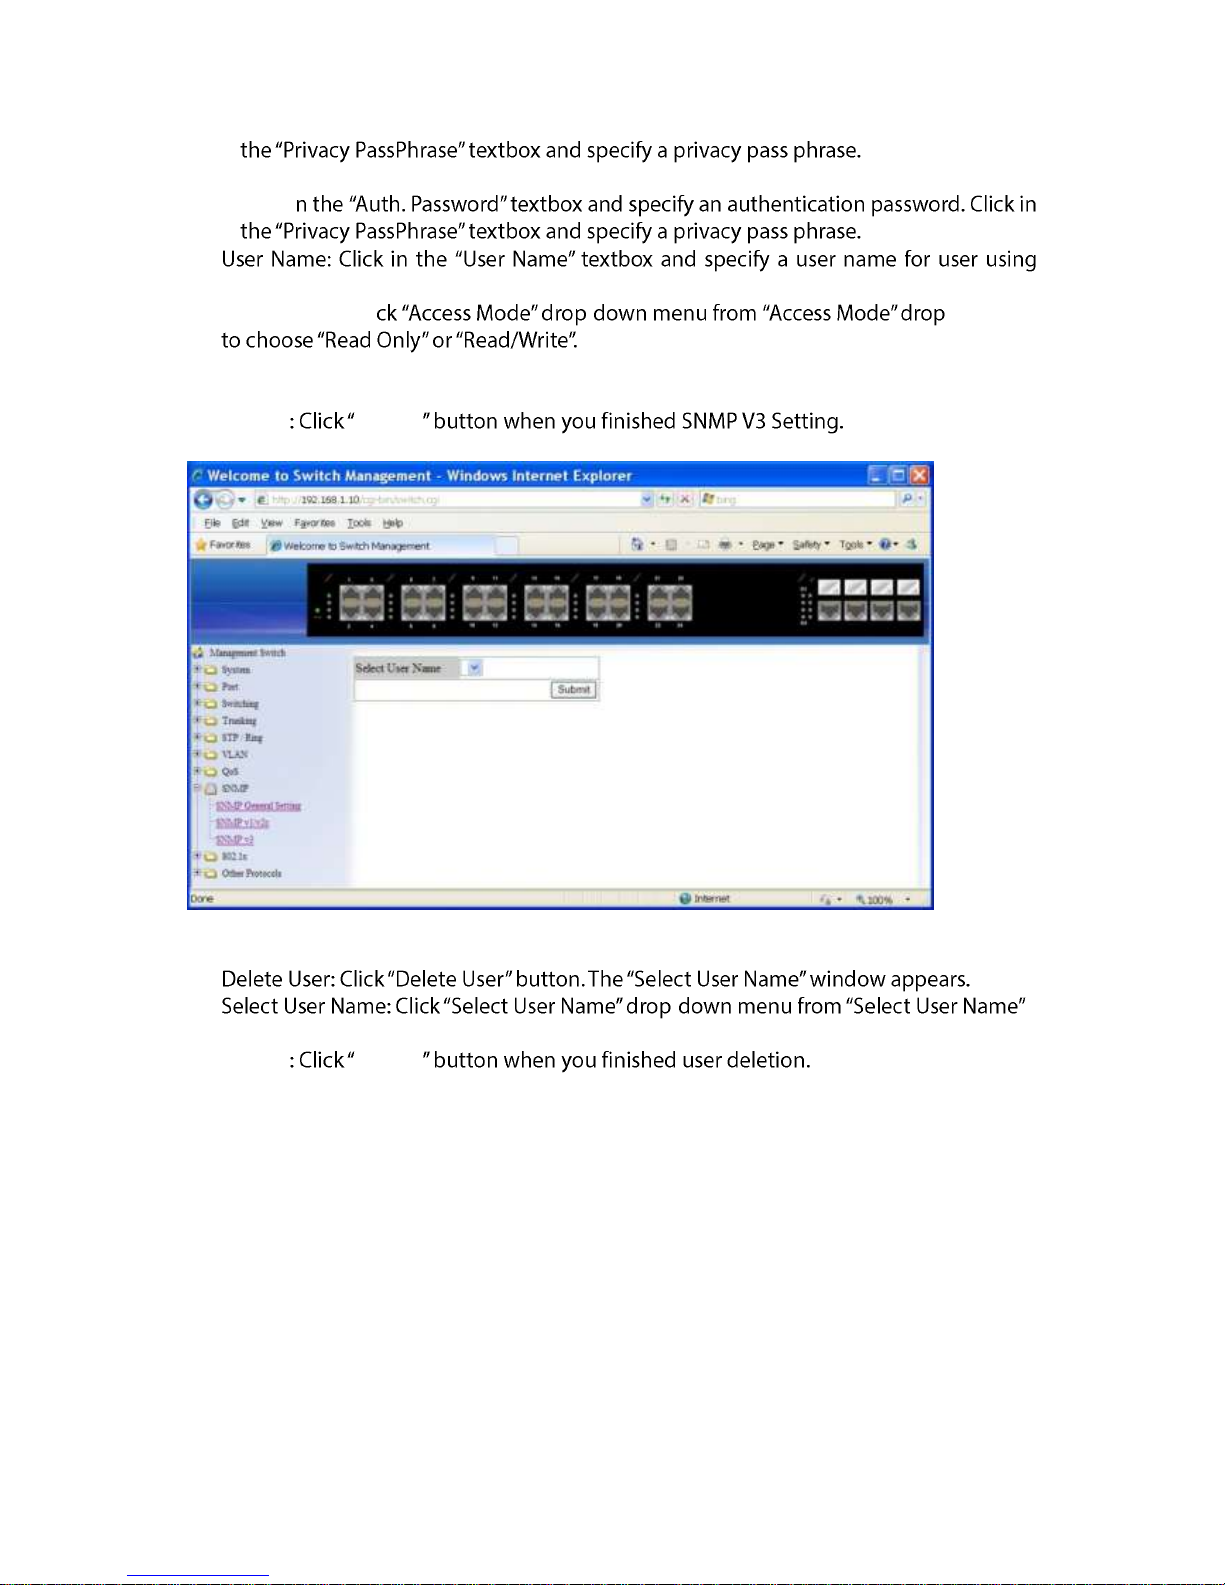
Delete User:
1.
2. drop-down list to choose the user to be deleted from using SNMP v3.
3. Submit Submit
Page 69
User Manual Page 69
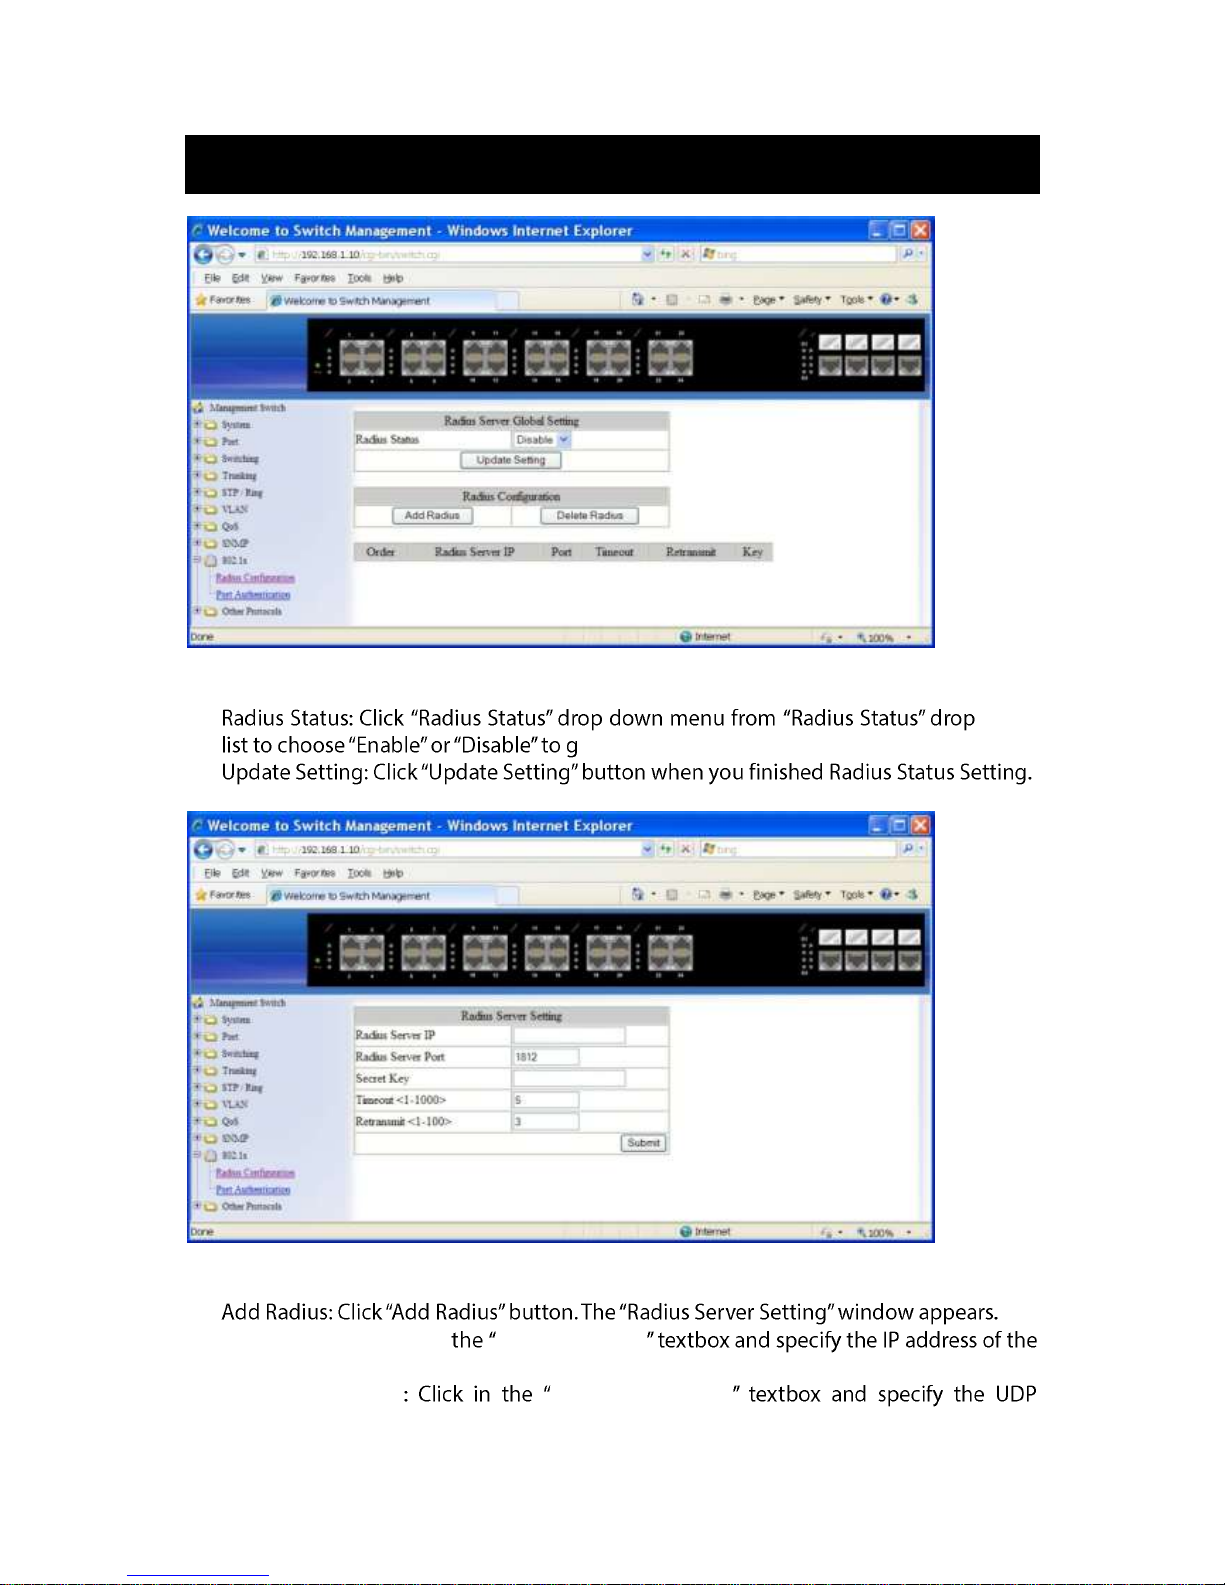
802.1x
Radius Configuration
1. - -down
lobally enable or disable authentication.
2.
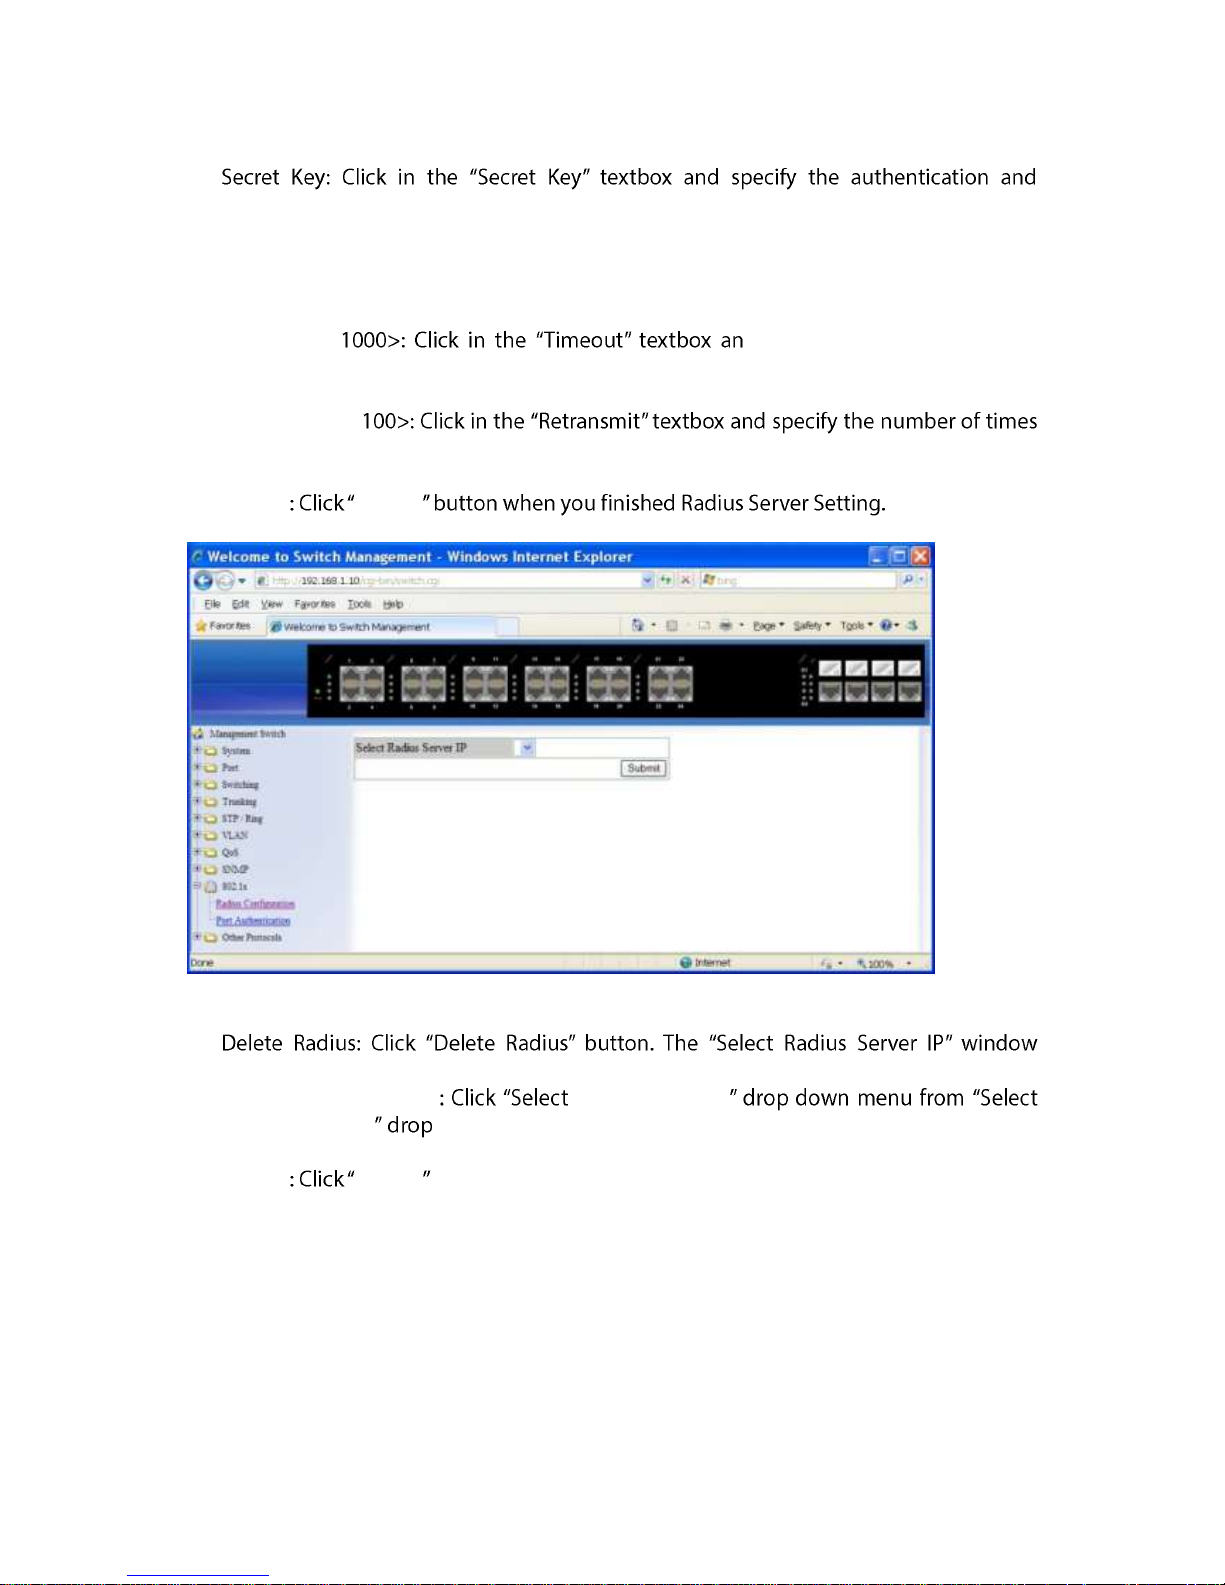
Add Radius:
1.
2. Radius Server IP: Click in Radius Server IP
remote radius server host.
3. Radius Server Port Radius Server Port
destination port for authentication requests. The host is not used for authentication if
Page 70
User Manual Page 70
set to 0.
4.
encryption key for all radius communications between the Switch and radius server.
This key must match the encryption used on the radius daemon. All leading spaces are
ignored, but spaces within and at the end of the key are used. If spaces are used in the
key, do not enclose the key in quotation marks unless the quotation marks themselves
are part of the key.
5. Timeout <1- d specify the time interval (in
seconds) that the Switch waits for the radius server to reply before retransmitting.
Enter a value in the range 1 to 1000.
6. Retransmit <1-
a radius request is resent to a server if that server is not responding or responding
slowly. Enter a value in the range 1 to 100.
7. Submit Submit
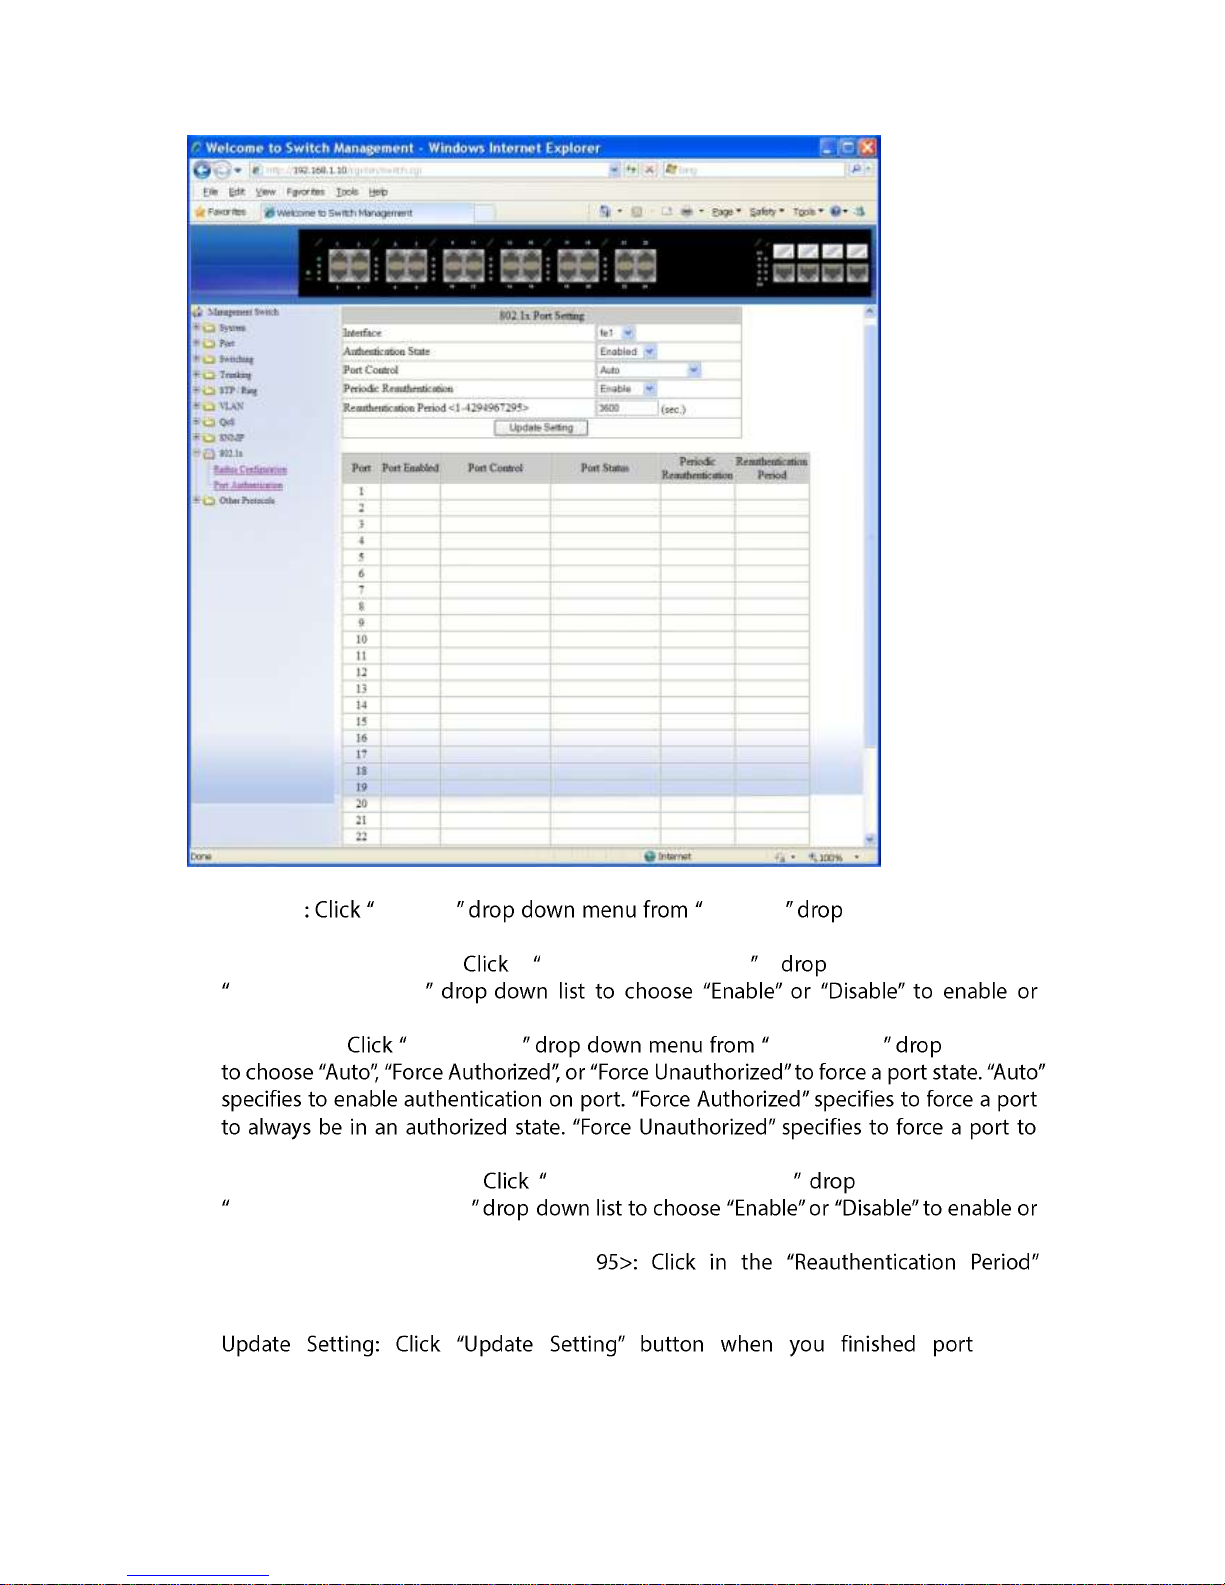
Delete Radius:
1.
appears.
2. Select Radius Server IP Radius Server IP -
Radius Server IP -down list to choose the IP address of the remote radius server
host to be deleted.
3. Submit Submit button when you finished radius server deletion.
Page 71
User Manual Page 71
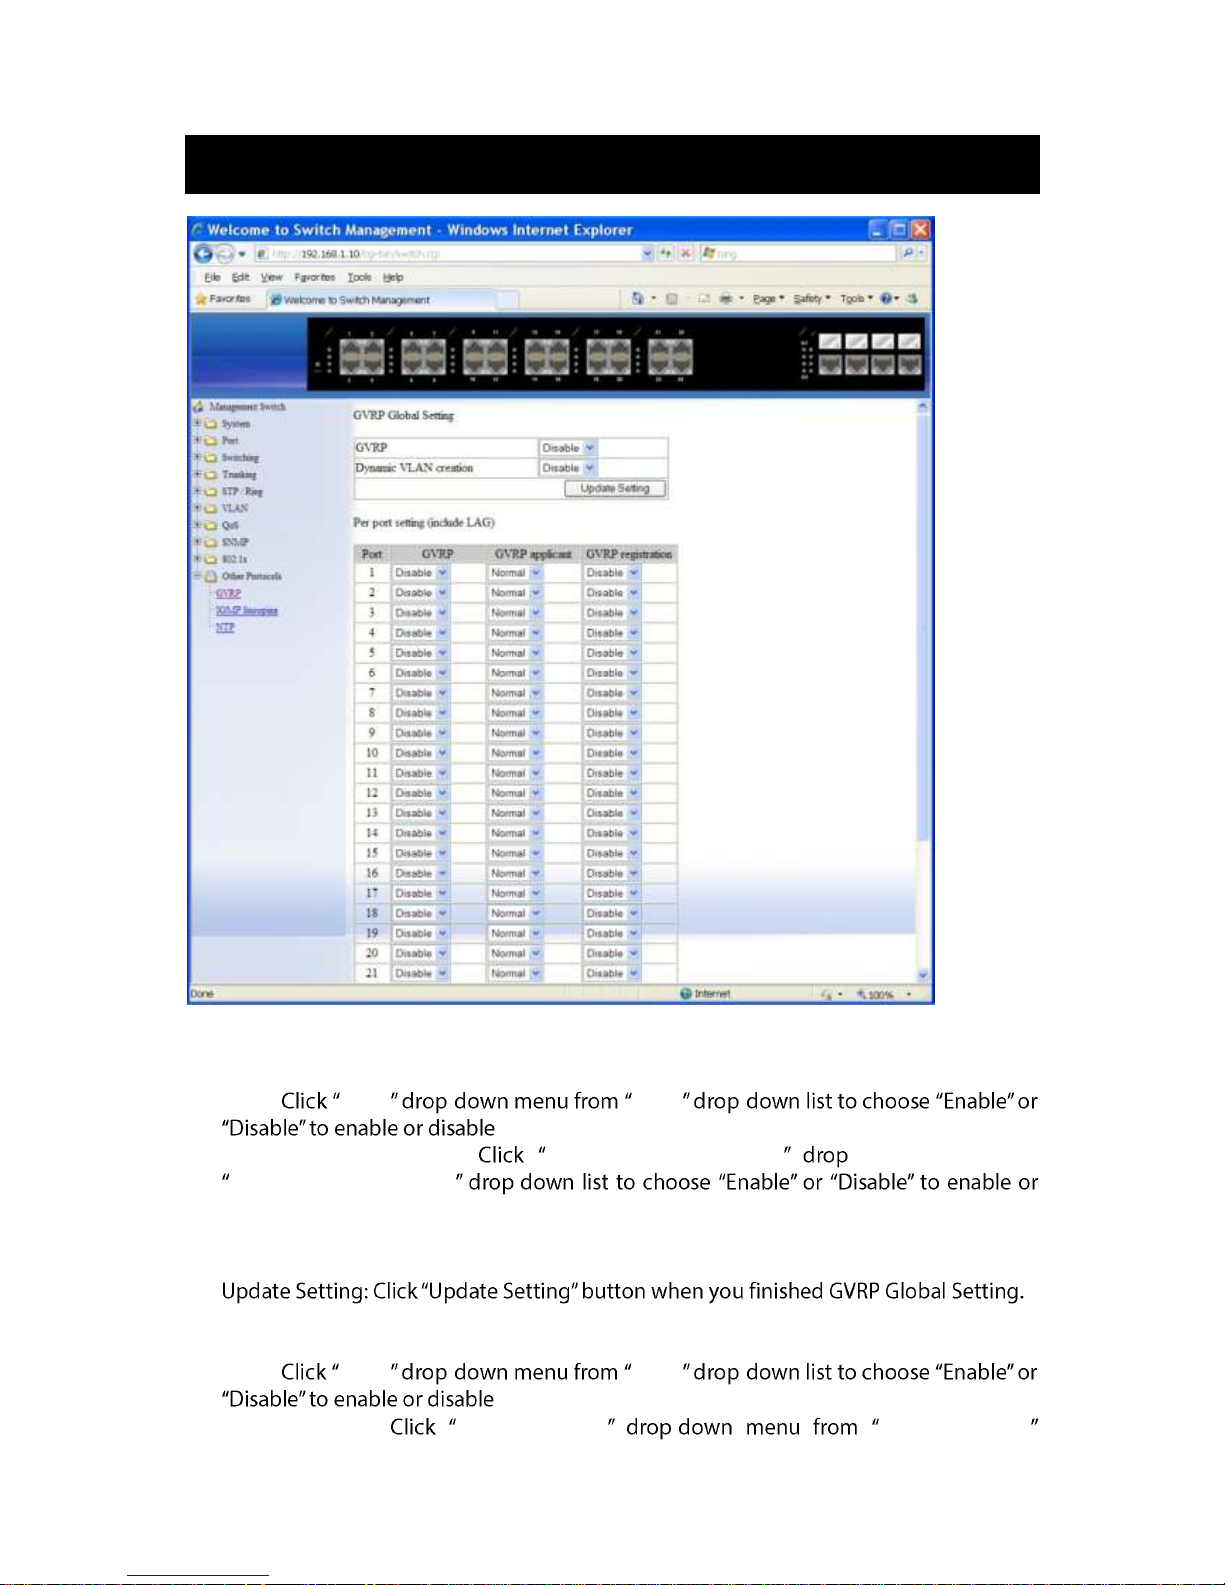
Port-Based Authentication
1. Interface Interface - Interface -down list to choose
the port to be set port-based authentication.
2. Authentication State: Authentication State -down menu from
Authentication State -
disable authentication state.
3. Port Control: Port Control - Port Control -down list
always be in an unauthorized state.
4. Periodic Reauthentication: Periodic Reauthentication -down menu from
Periodic Reauthentication -
disable periodic reauthentication.
5. Reauthentication Period <1-42949672
textbox and specify the seconds between reauthorization attempts. The default time is
3600 seconds.
6. -based
authentication setting.
Page 72
User Manual Page 72
Other Protocols
GVRP
GVRP Global Setting:
1. GVRP: GVRP - GVRP -
GVRP (GARP VLAN Registration Protocol).
2. Dynamic VLAN creation: Dynamic VLAN creation -down menu from
Dynamic VLAN creation disable Dynamic VLAN creation. GARP (Generic Attribute Registration Protocol)
provides IEEE802.1Q compliant VLAN pruning and dynamic VLAN creation on
IEEE802.1Q trunk ports.
3.
Per port setting (include LAG):
1. GVRP: GVRP - GVRP -
GVRP for the port.
2. GVRP applicant: GVRP applicant - GVRP applicant
Page 73
User Manual Page 73
drop- . Ports in the GVRP active
applicant state send GVRP VLAN declarations when they are in the STP (Spanning Tree
Protocol) blocking state, which prevents the STP bridge protocol data units (BPDUs)
from being pruned from the other port. Ports in the GVRP normal applicant state do
not declare GVRP VLANs when in the STP blocking state.
3. GVRP registration: GVRP registration - GVRP registration
drop- GVRP registration to
the port. Configuring an IEEE802.1Q trunk port in registration mode allows dynamic
creation (if dynamic VLAN creation is enabled), registration, and deregistration of
VLANs on the trunk port.
4.
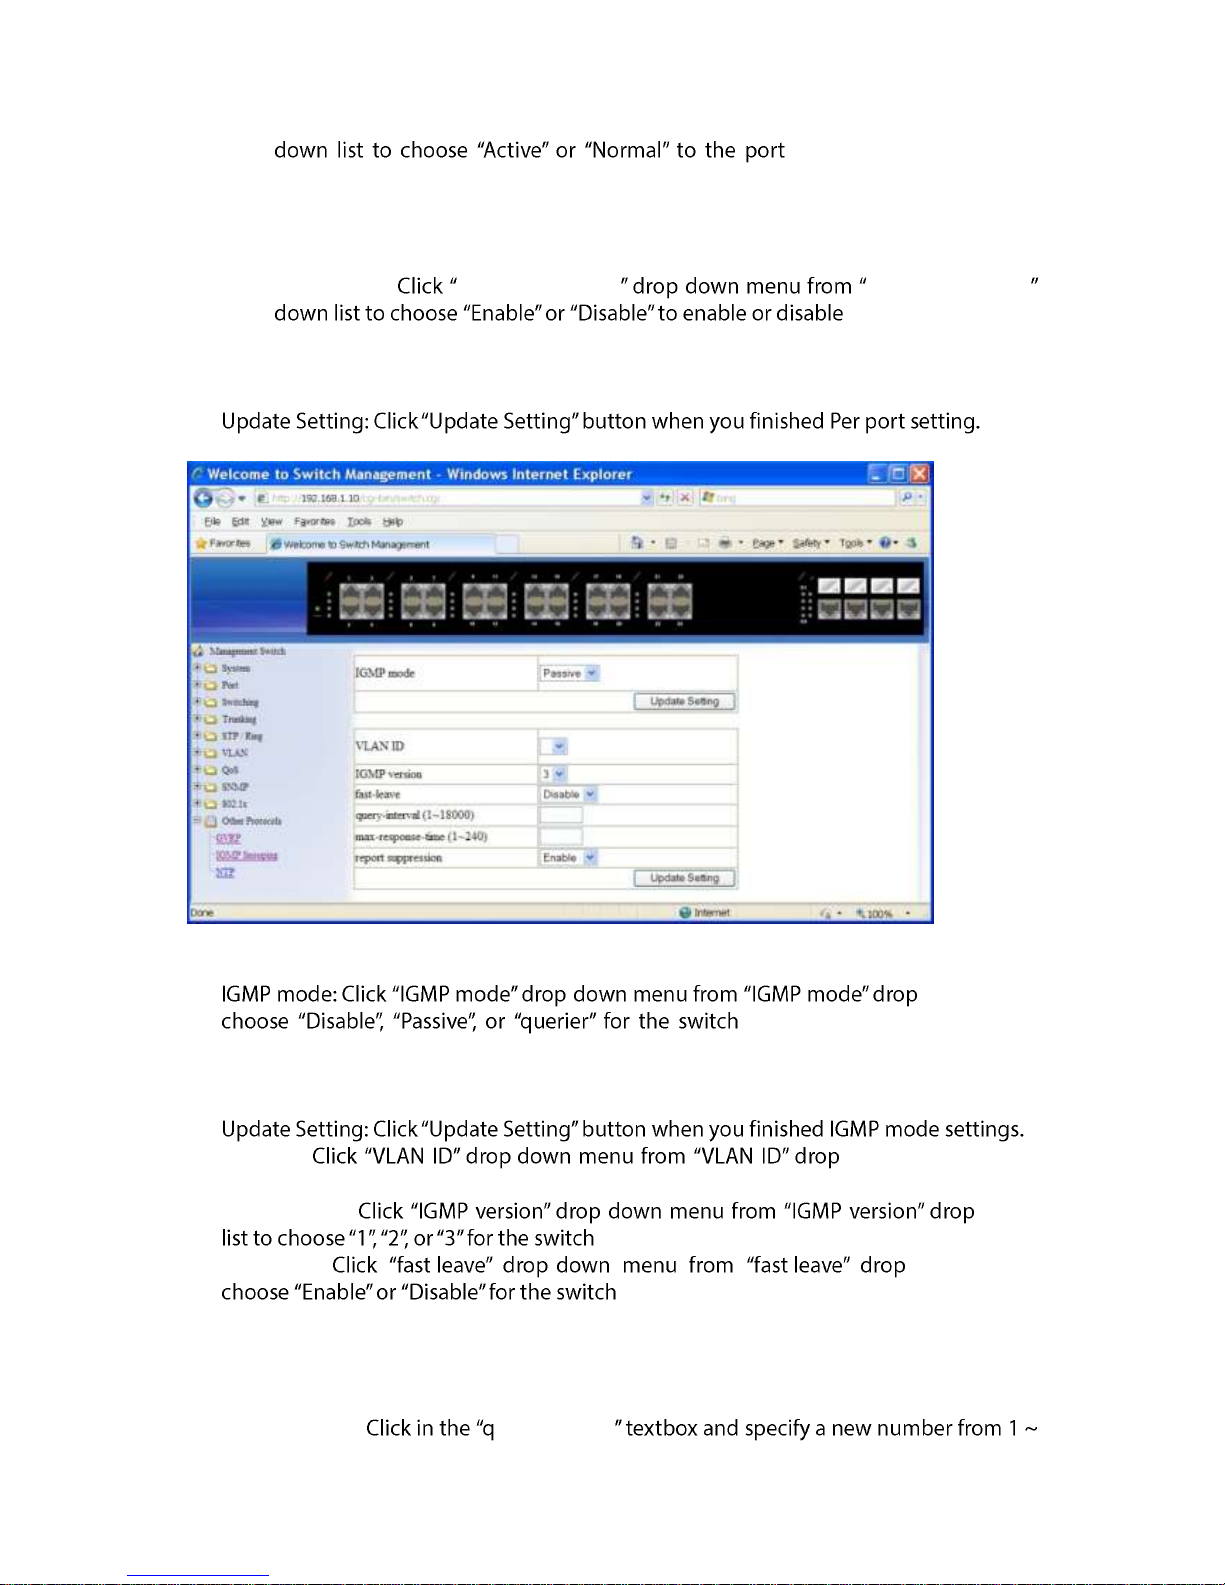
IGMP Snooping
1. - -down list to
. Disable: Disable IGMP on the
switch. Passive: The switch with only multicast-data-forwarding capability. Querier: The
switch acts as the querier for the network. There is only one querier on a network at
any time.
2.
3. VLAN ID: - -down list to choose
the VLAN under configuration for the switch.
4. IGMP version: - -down
.
5. Fast-leave: - - - -down list to
. Enable this function will allow members of a
multicast group to leave the group immediately when an IGMP Leave Report Packet is
received by the Switch.
IGMP querier:
1. Query-interval: uery-interval
Page 74
User Manual Page 74
18000. The query-interval field is used to set the time (in seconds) between
transmitting IGMP queries. Entries between 1 and 18000 seconds are allowed. Default
= 125.
2. Max-response-time: max-response-time
number from 1 ~ 124. This determines the maximum amount of time in seconds
allowed before sending an IGMP response report. The max-response-time field allows
an entry between 1 and 124 (seconds). Default = 10.
IGMP passive snooping:
1. Report suppression: eport suppression -down m eport
suppression - . Use this
command to enable report suppression for IGMP version 1 and version 2. Report
suppression does not apply to IGMP version 3, and is turned off by default for IGMP
version 1 and IGMP version 2 reports. The switch uses IGMP report suppression to
forward only one IGMP report per multicast router query to multicast devices. When
IGMP router suppression is enabled, the switch sends the first IGMP report from all
hosts for a group to all the multicast routers. The switch does not send the remaining
IGMP reports for the group to the multicast routers. This feature prevents duplicate
reports from being sent to the multicast devices.
2.
Page 75
User Manual Page 75
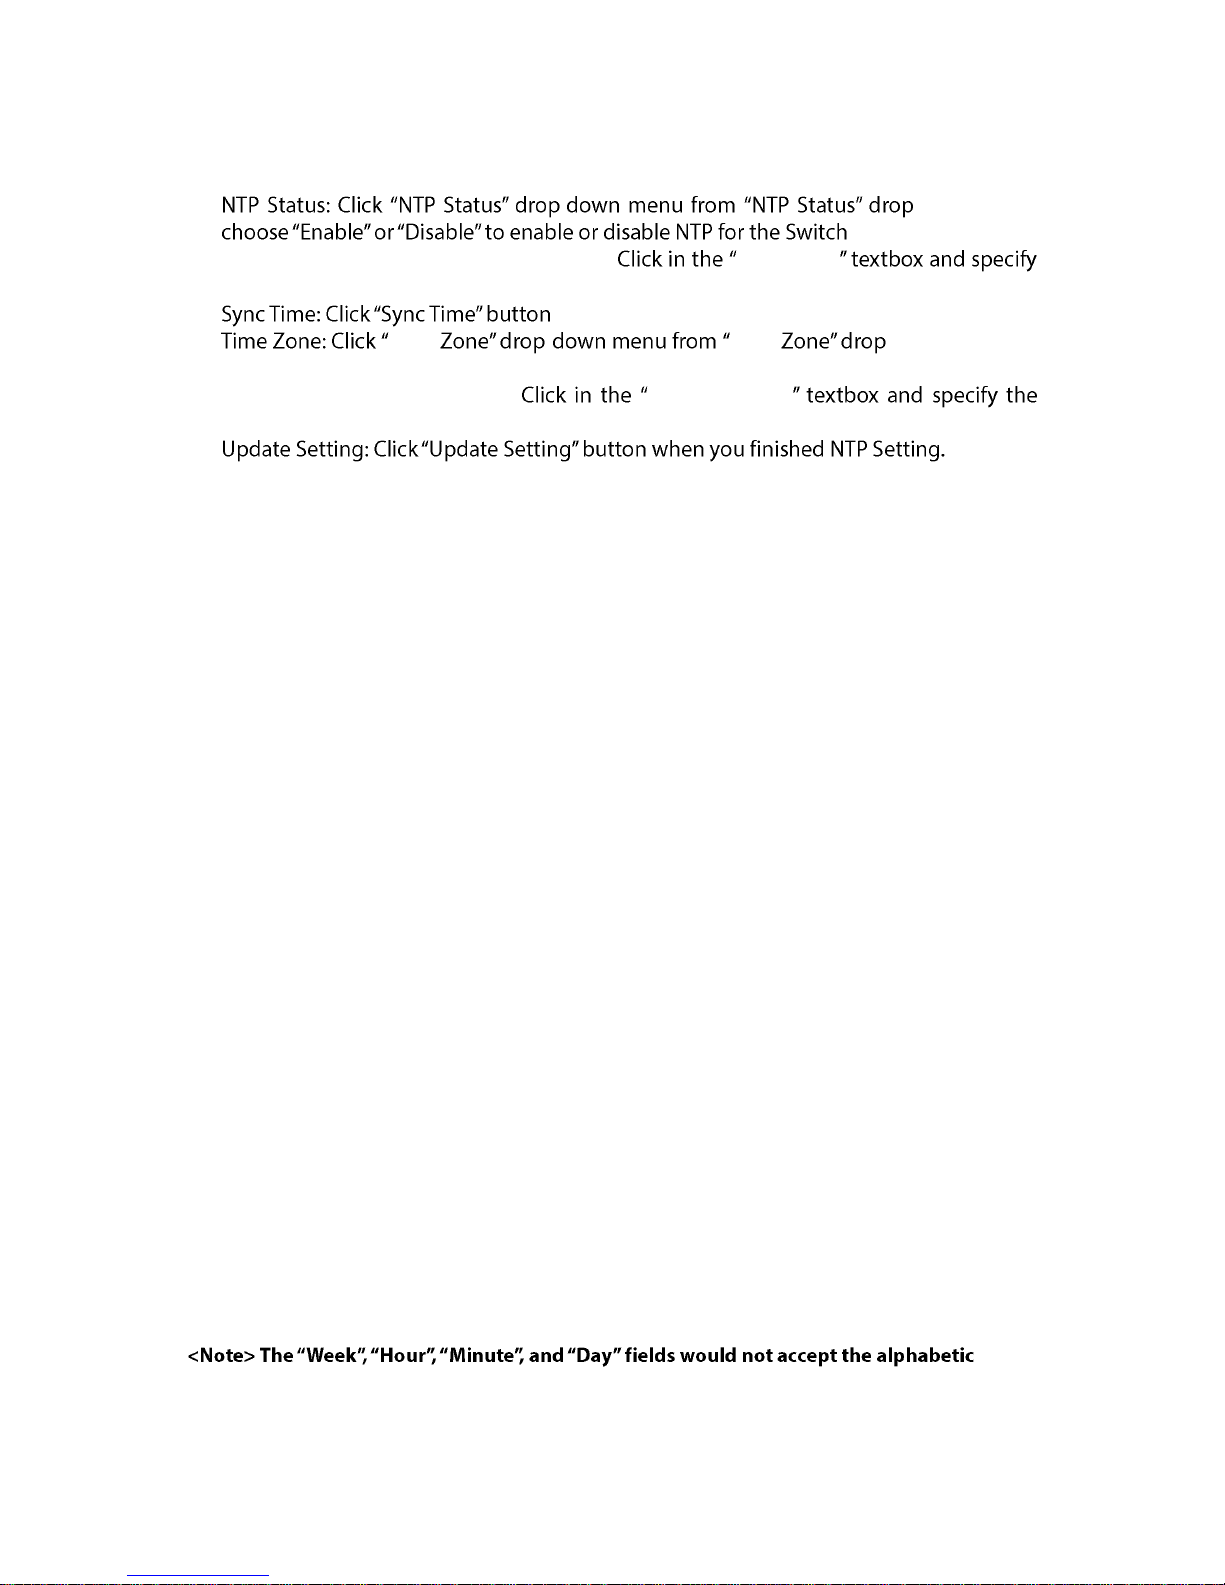
NTP
NTP Setting:
1. - -down list to
.
2. NTP Server (IP Address or Domain name): NTP Server
the IP address or Domain name of NTP server.
3. to synchronize time with NTP server.
4. Time - Time -down list to set
time zone.
5. Polling Interval (1-10080 min): Polling Interval
polling interval.
6.
Daylight Saving Setting:
1. Daylight Saving Mode: Click "Daylight Saving Mode" drop-down menu from "Daylight
Saving Mode" drop-down list to choose "Disable", "Weekday", or "Date" to choose
disable, weekday, or date daylight saving for the Switch.
2. Time Set Offset (1-1440 min): Click in the "Time Set Offset" textbox and specify the
offset time of daylight saving. For example enter 60 for one hour offset.
3. Daylight Saving Time zone: Click in the "Daylight Saving Time zone" textbox and
specify the daylight saving time zone. This can be any given name in 14-character
alpha-numerical. Enter the Daylight-Saving time zone using the following example:
EDT - East Daylight Saving Time Zone.
CDT - Central Daylight-Saving Time Zone.
MDT - Mountain Daylight-Saving Time Zone.
PDT - Pacific Daylight-Saving Time Zone.
ADT - Alaska Daylight-Saving Time Zone.
4. Weekday: Click in the textboxes and specify the daylight saving period.
Month: Click "Month" drop-down menu from "Month" drop-down list to choose
from January to December.
Week: <1-5> Specifies weekdays from Monday to Friday.
Day: Click "Day" drop-down menu from "Day" drop-down list to choose from
Sunday to Saturday.
Hour: <0-23> Specifies from 0 to 23.
Minute: <0-59> Specifies from 0 to 59.
5. Date: Click in the textboxes and specify the daylight saving period.
Month: Click "Month" drop-down menu from "Month" drop-down list to choose
from January to December.
Day: <1-31> Specifies from 1 to 31.
Hour: <0-23> Specifies from 0 to 23.
Minute: <0-59> Specifies from 0 to 59.
6. Update Setting: Click "Update Setting" button when you finished Daylight Saving
Setting.
characters (Like Jan, Feb, sun, mon). They only accept the two digit numbers (0 through 9).
Page 76
User Manual Page 76
Command Line Console Management
The switch provides a command line console interface for configuration purposes. The
switch can be configured either locally through its RS-232 port or remotely via a Telnet
session. For the later, you must specify an IP address for the switch first.
This chapter describes how to configure the switch using its console by Commend Line.
Administration Console
Connect the DB9 straight cable to the RS-232 serial port of the device to the RS-232 serial
port of the terminal or computer running the terminal emulation application.
Direct access to the administration console is achieved by directly connecting a terminal
or a PC equipped with a terminal-emulation program (such as HyperTerminal) to the
switch console port.
When using the management method, configure the terminal-emulation program to use
the following parameters (you can change these settings after login):
[Default parameters]
115,200bps
8 data bits
No parity
1 stop bit
Page 77
User Manual Page 77
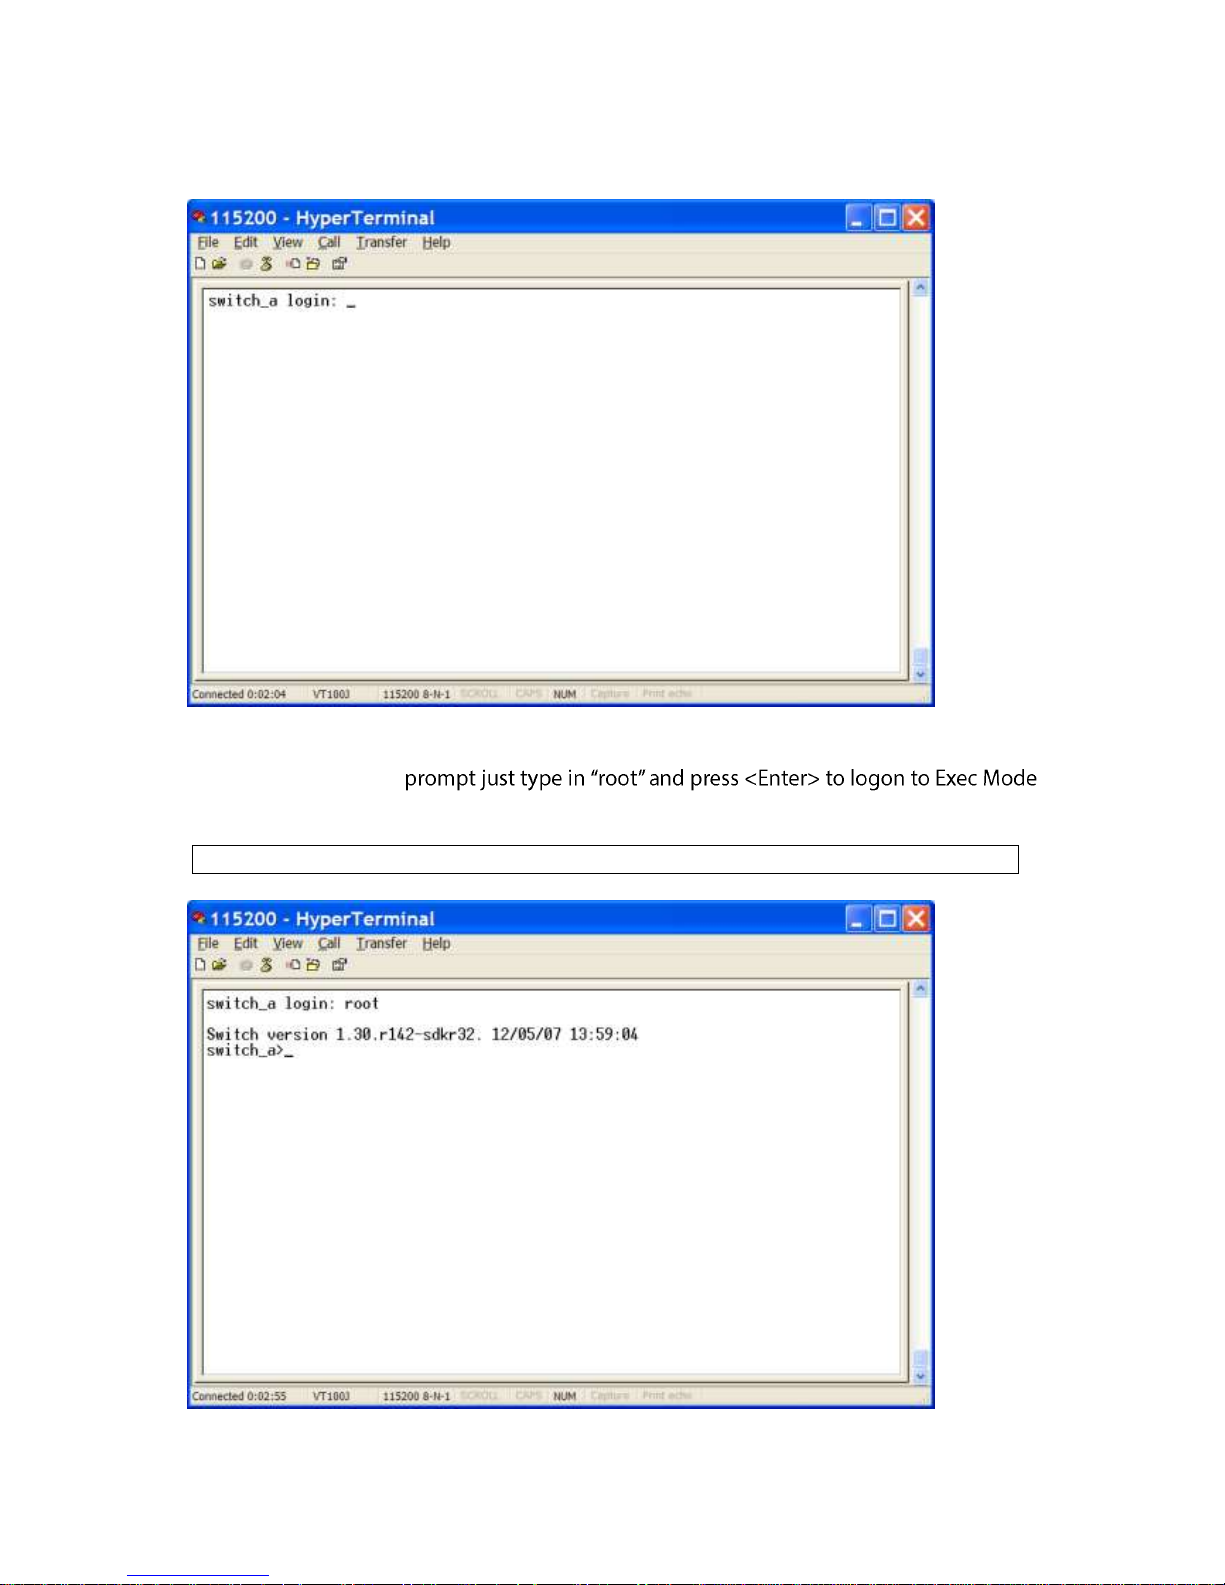
Exec Mode (View Mode)
Logon to Exec Mode (View Mode)
At the switch_a login:
(or View Mode).
switch_a login: root
Page 78
User Manual Page 78
Basic commands
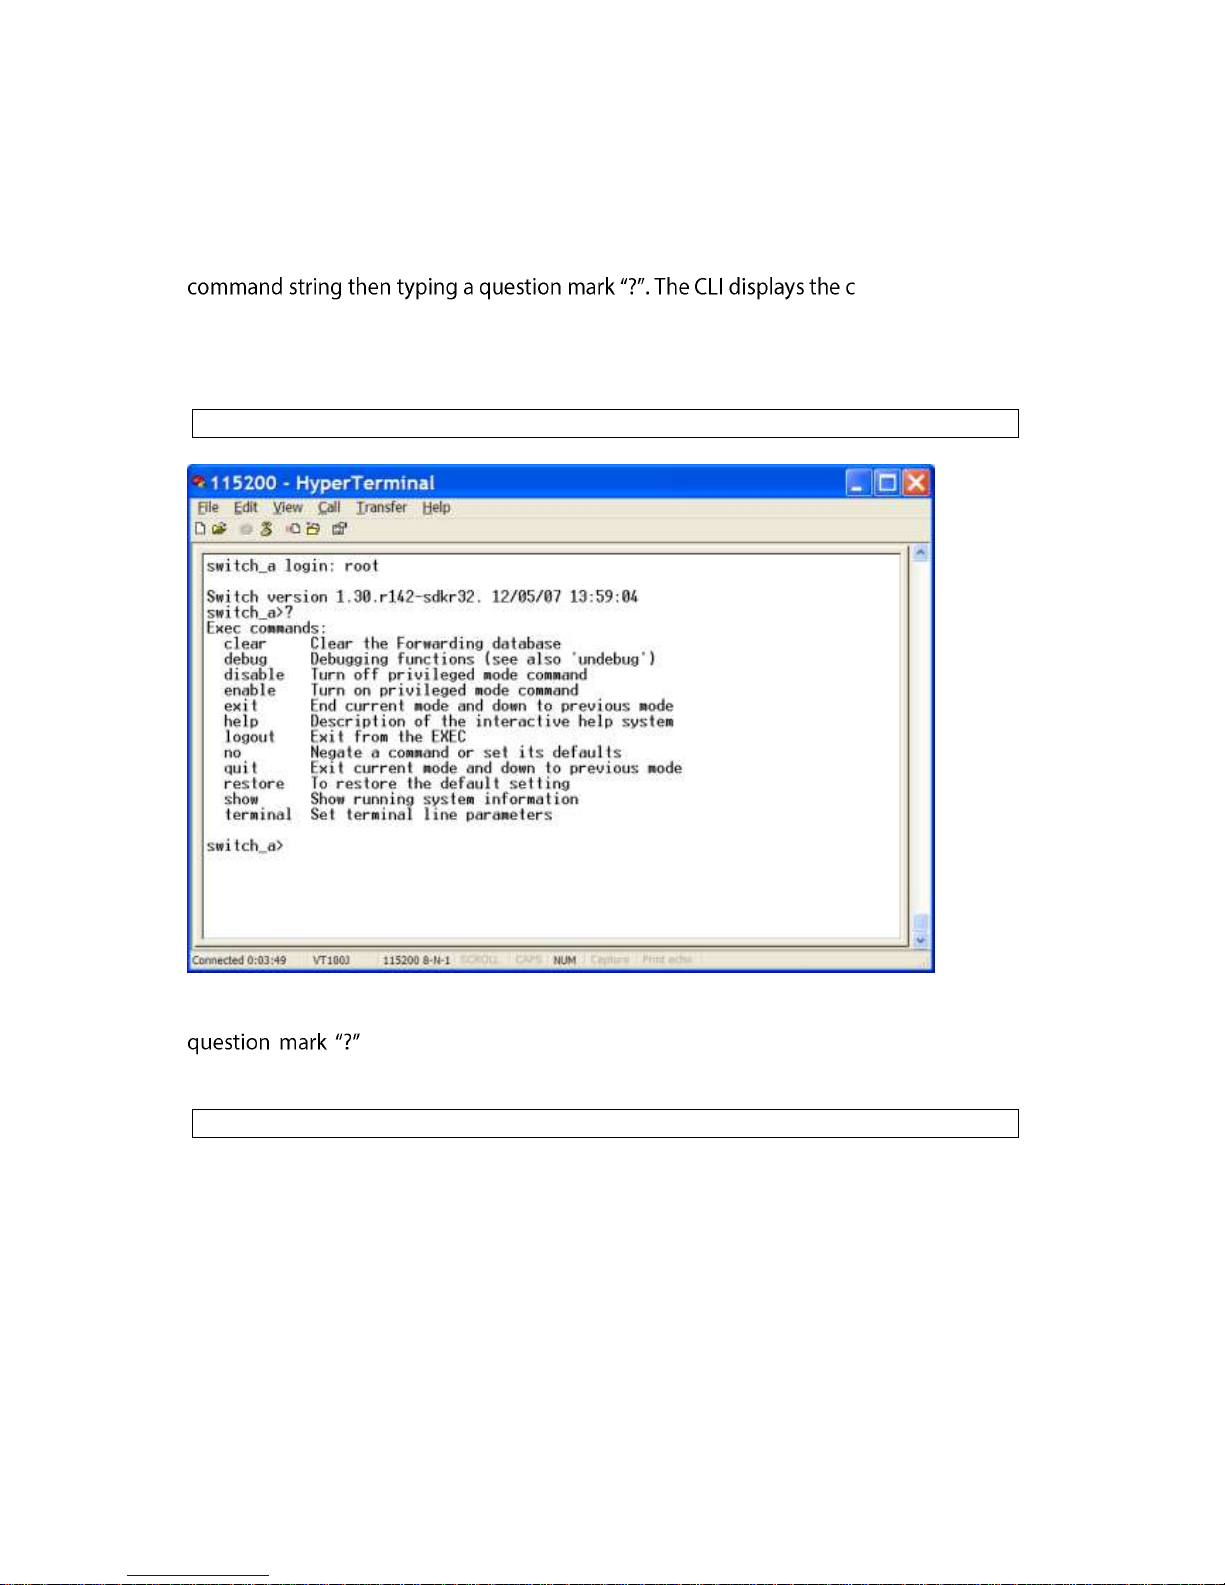
Exec Mode (or View Mode) is the base mode from where users can perform basic
commands like:
clear, debug, disable, enable, exit, help, logout, no, quit, show, terminal
The CLI contains a text-based help facility. Access this help by typing in the full or partial
ommand keywords
or parameters along with a short description.
At the switch_a> prompt just press <?> to list the above basic commands.
switch_a>?
At the switch_a> prompt just type in the full or partial command string then typing a
to display the command keywords or parameters along with a short
description.
switch_a>show ?
Page 79
User Manual Page 79
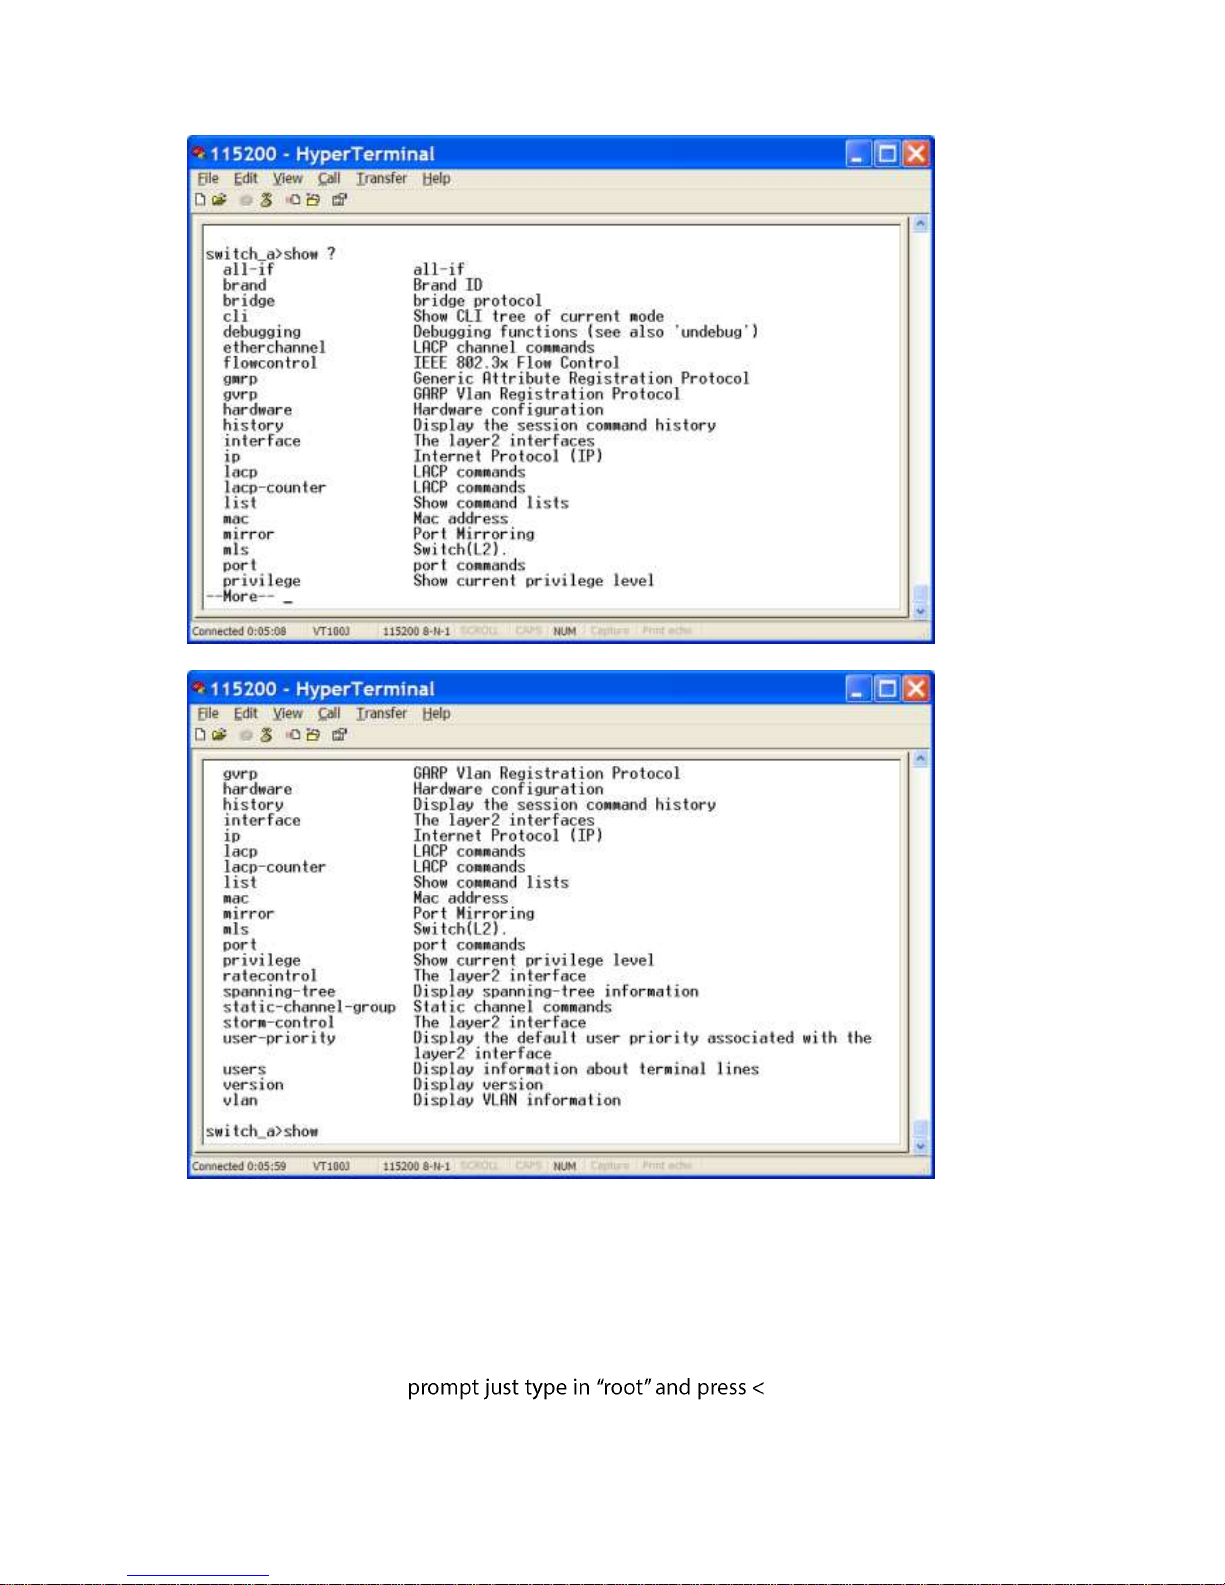
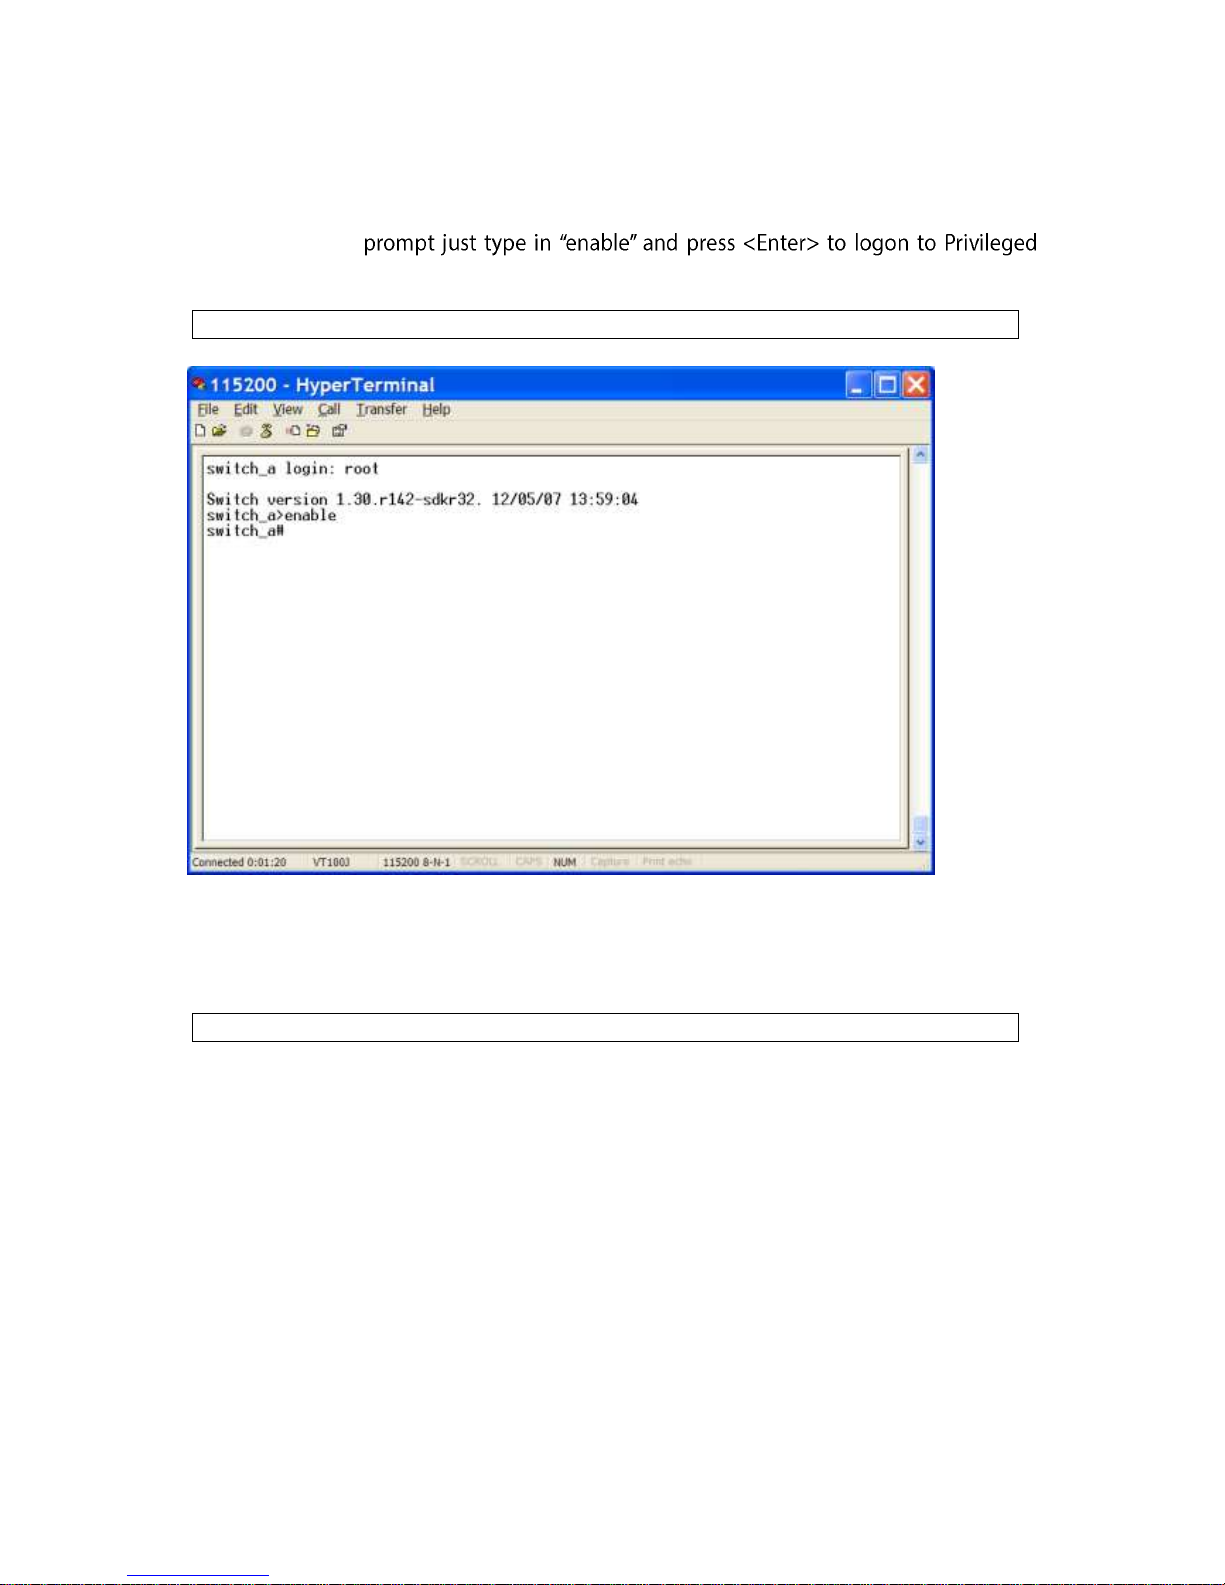
Login timed out
The login session to Exec Mode (or View Mode) has timed out due to an extended period
of inactivity (60 seconds) to indicate authentication attempt timed out. And the switch_a
login: prompt will show on the screen.
Logon back to Exec Mode (View Mode)
At the switch_a login: Enter> to logon back to Exec
Mode (or View Mode).
Page 80
User Manual Page 80
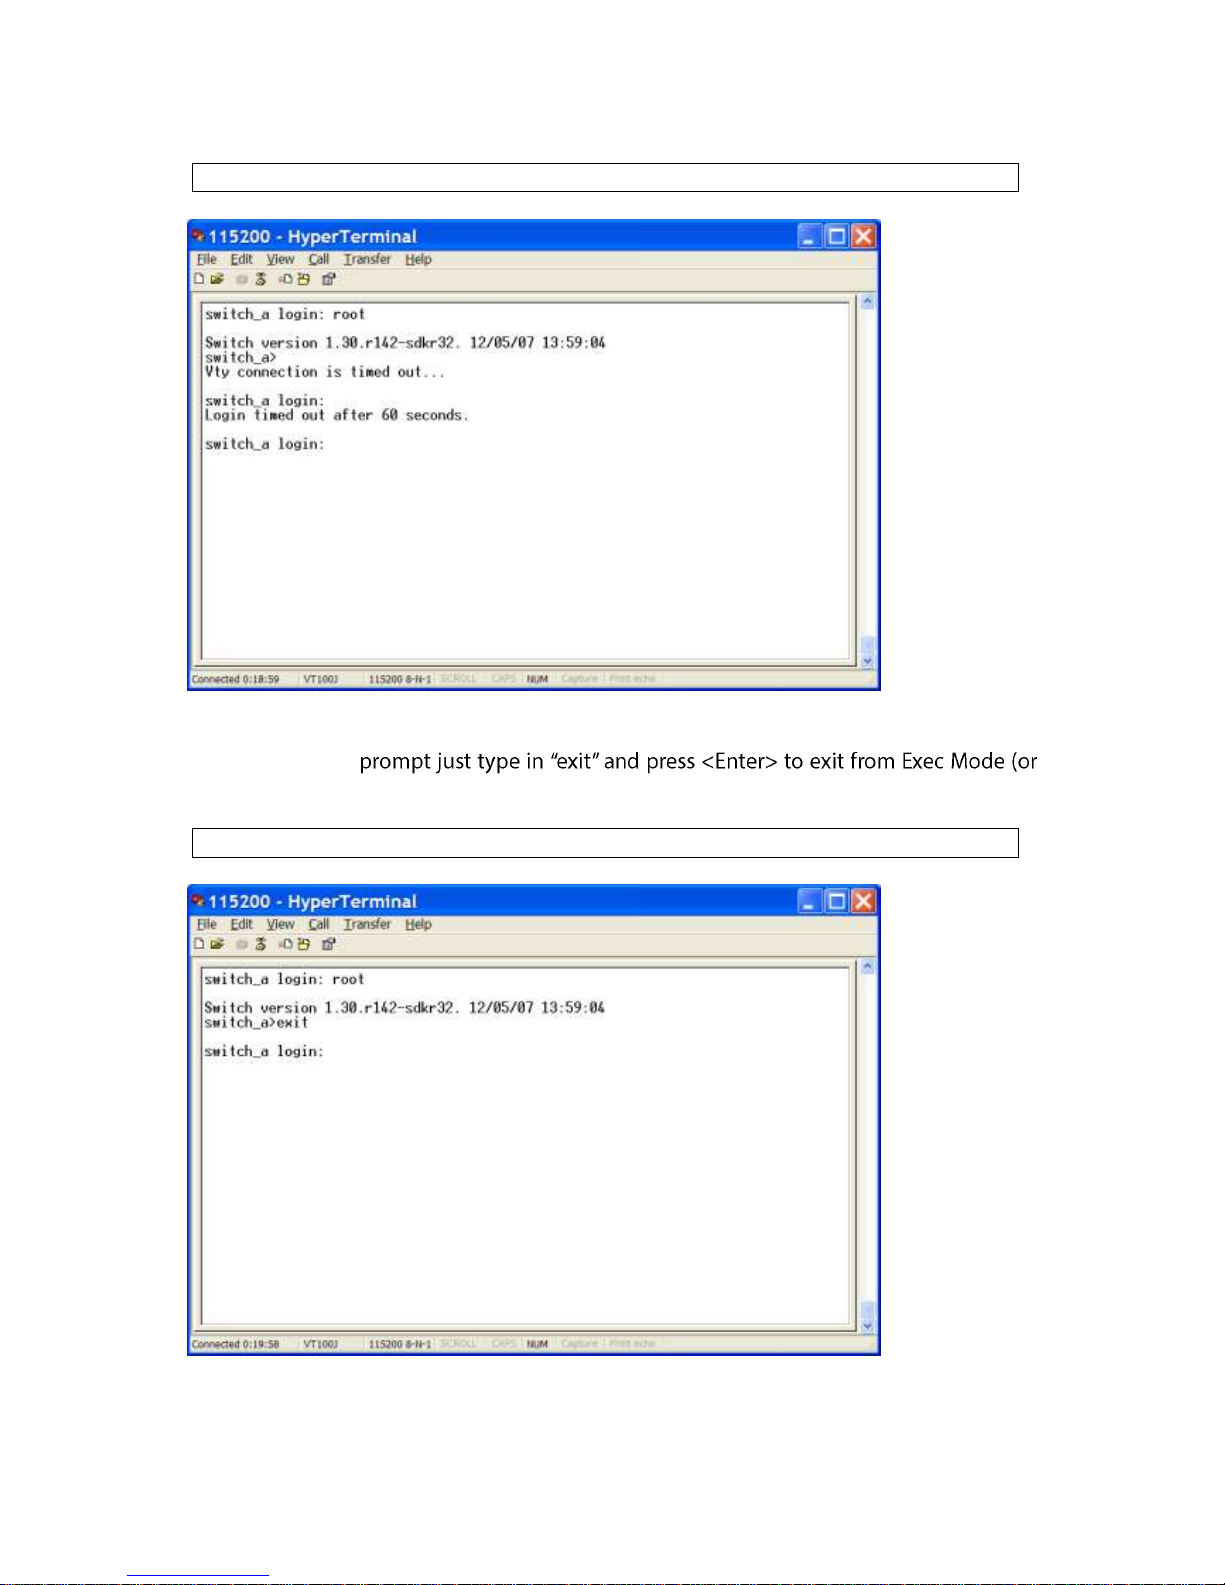
switch_a login: root
Exit from Exec Mode (View Mode)
At the switch_a>
View Mode).
switch_a>exit
Page 81
User Manual Page 81
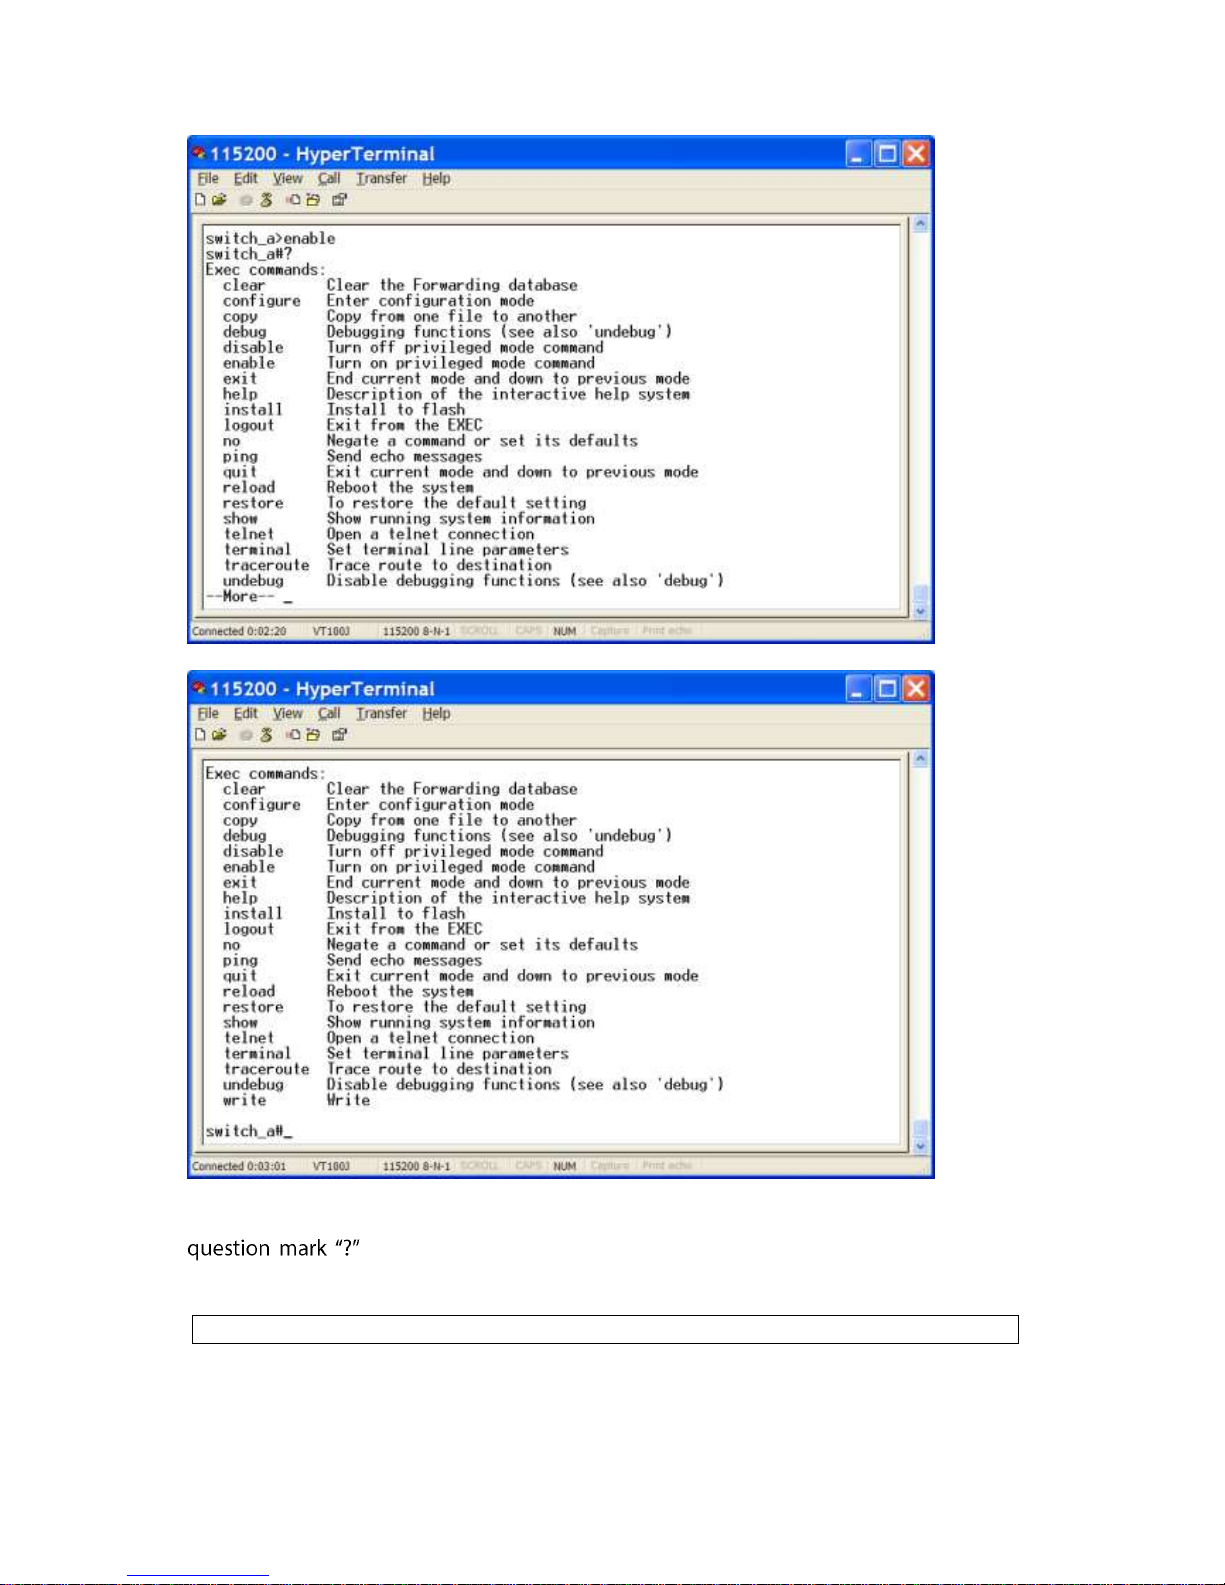
Privileged Exec Mode (Enable Mode)
Logon to Privileged Exec Mode (Enable Mode)
At the switch_a>
Exec Mode (or Enable Mode). And the switch_a# prompt will show on the screen.
switch_a>enable
Commands
Privileged Exec Mode (or Enable Mode) allows users to run commands as following.
At the switch_a# prompt just press <?> to list the commands.
switch_a#?
Page 82
User Manual Page 82
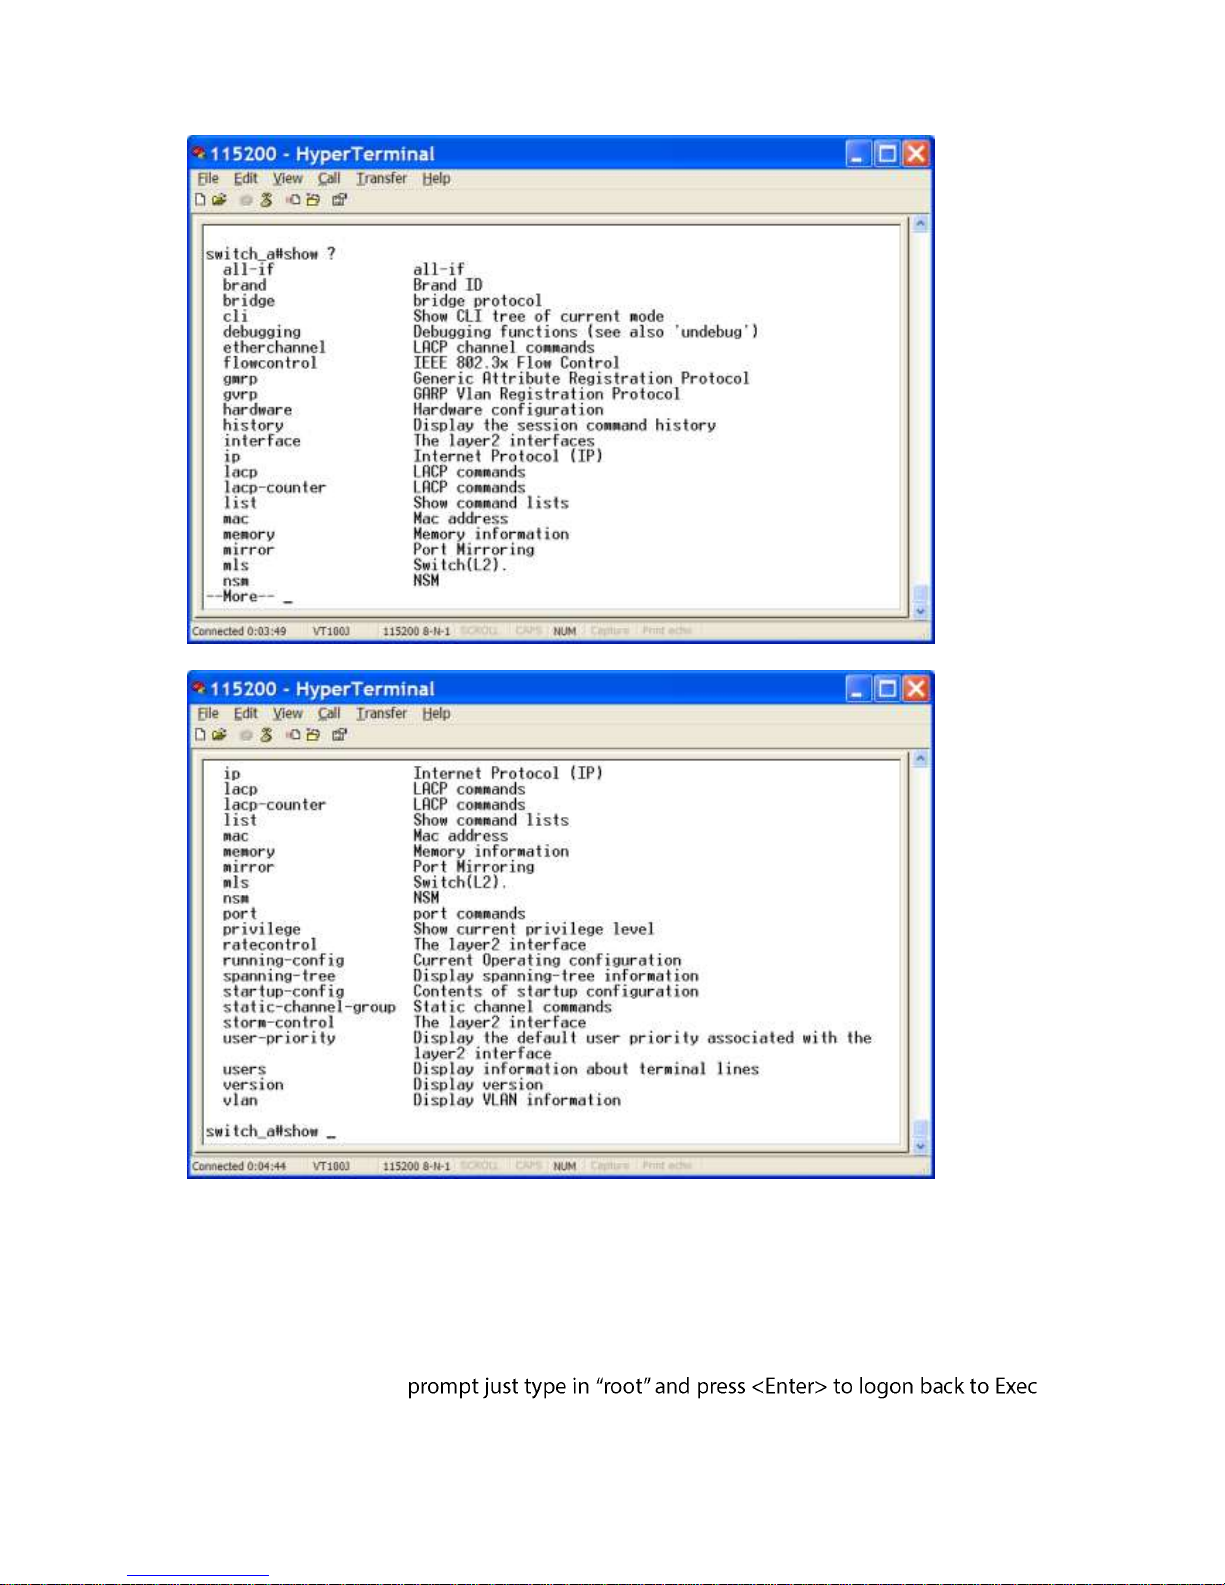
At the switch_a# prompt just type in the full or partial command string then typing a
to display the command keywords or parameters along with a short
description.
switch_a#show ?
Page 83
User Manual Page 83
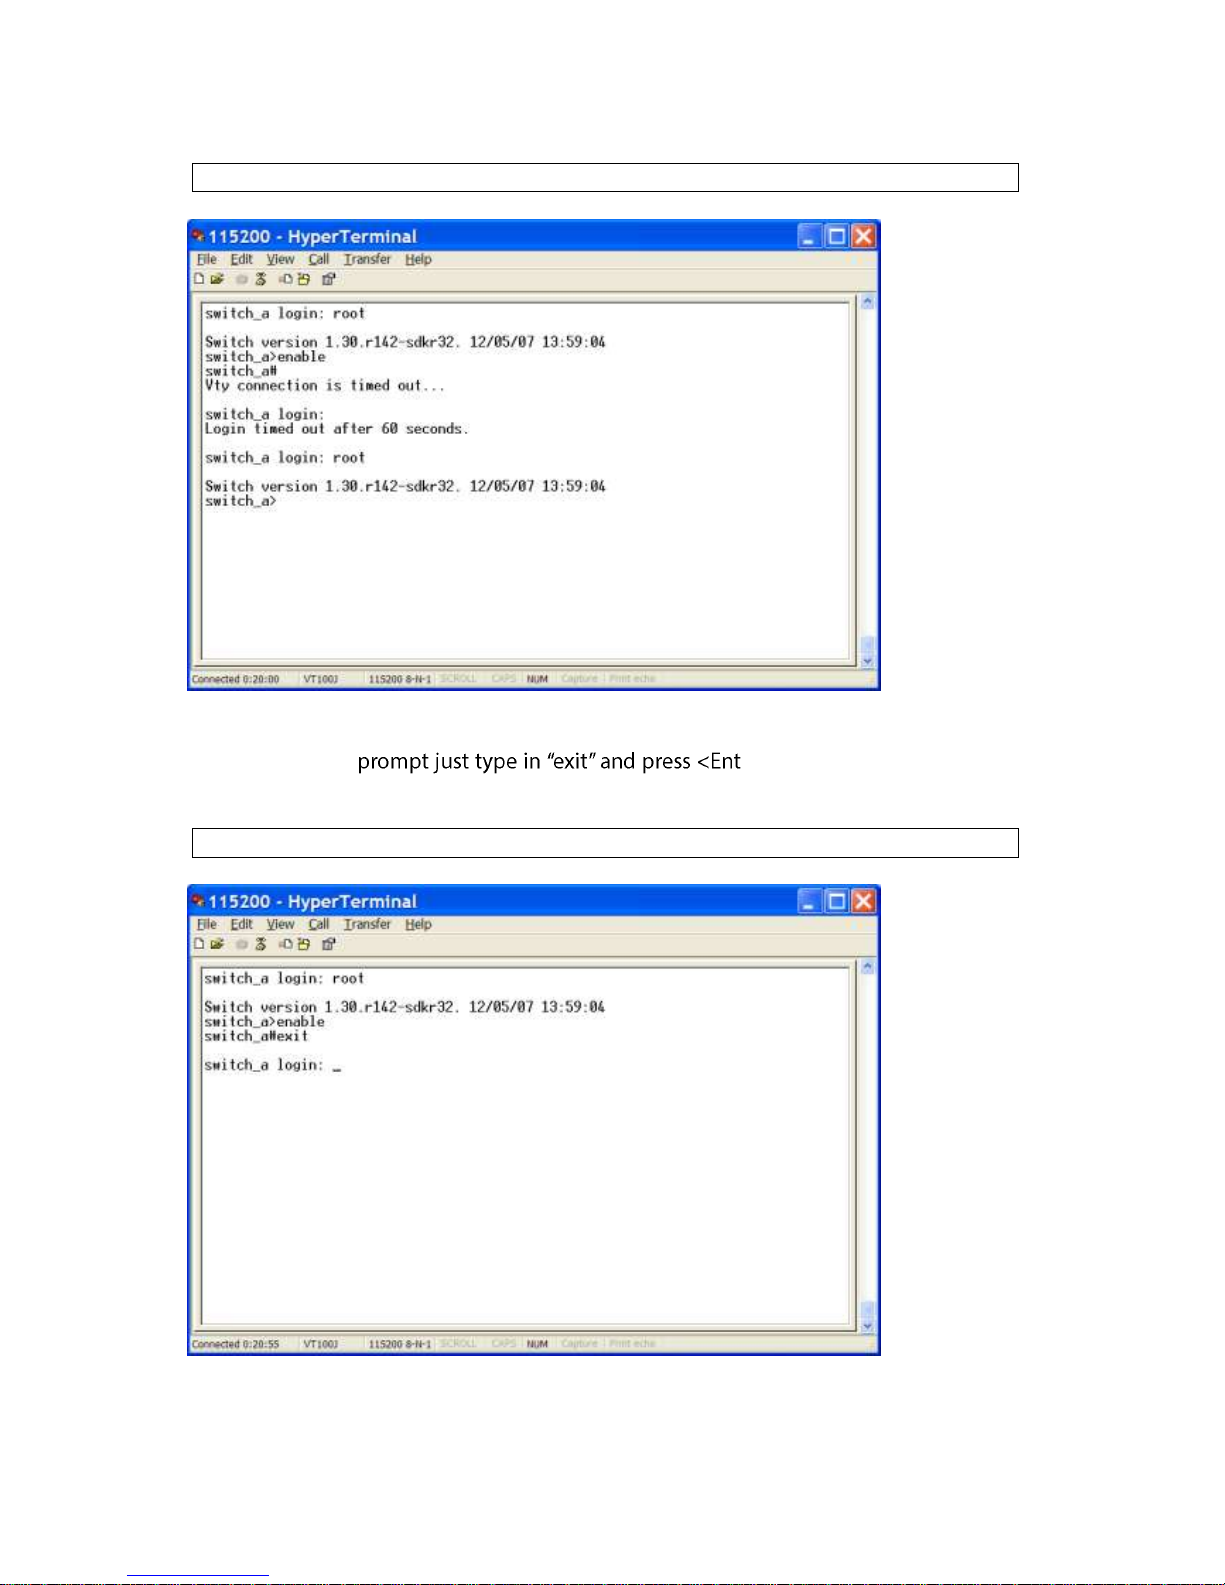
Login timed out
The login session to Privileged Exec Mode (or Enable Mode) has timed out due to an
extended period of inactivity (60 seconds) to indicate authentication attempt timed out.
And the switch_a login: prompt will show on the screen.
Logon back to Exec Mode (View Mode)
At the switch_a login:
Mode (or View Mode).
Page 84
User Manual Page 84
switch_a login: root
Exit from Privileged Exec Mode (or Enable Mode)
At the switch_a# er> to exit from Privileged Exec
Mode (or Enable Mode).
switch_a#exit
Page 85
User Manual Page 85
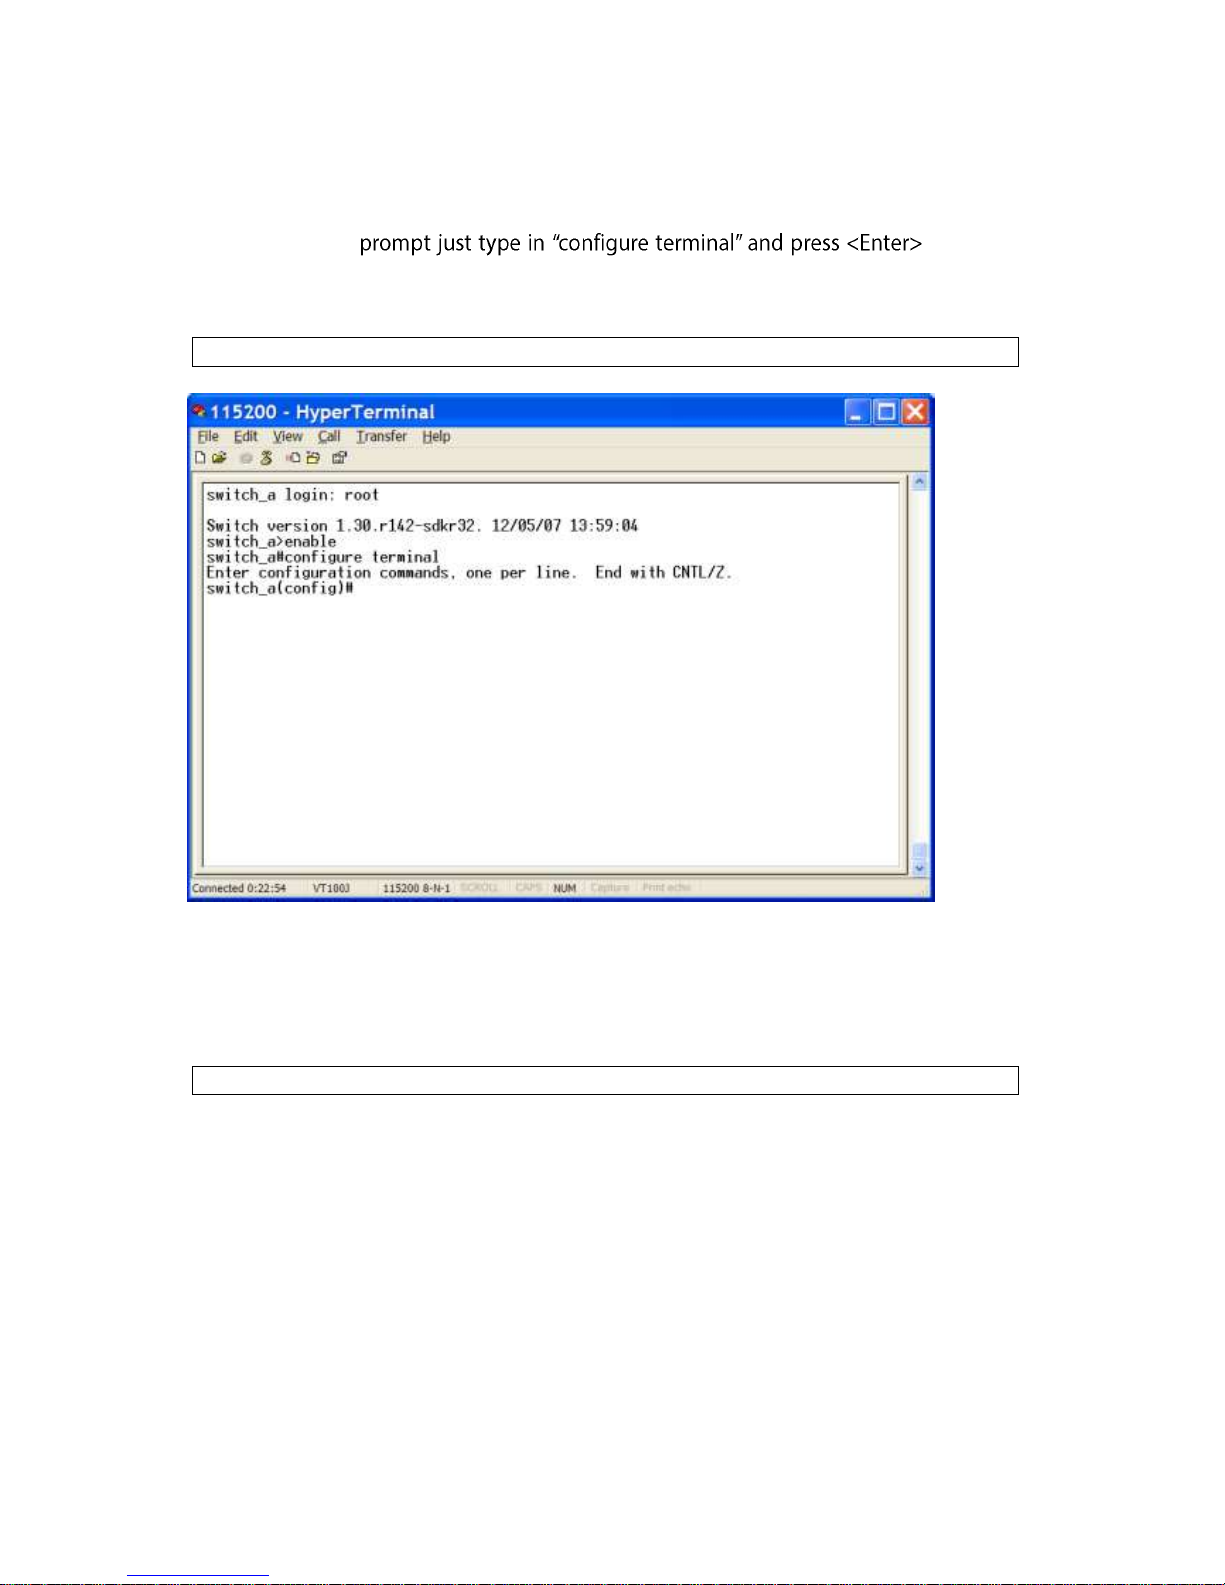
Configure Mode (Configure Terminal Mode)
Logon to Configure Mode (Configure Terminal Mode)
At the switch_a# to logon to
Configure Mode (or Configure Terminal Mode). And the switch_a(config)# prompt will
show on the screen.
switch_a#configure terminal
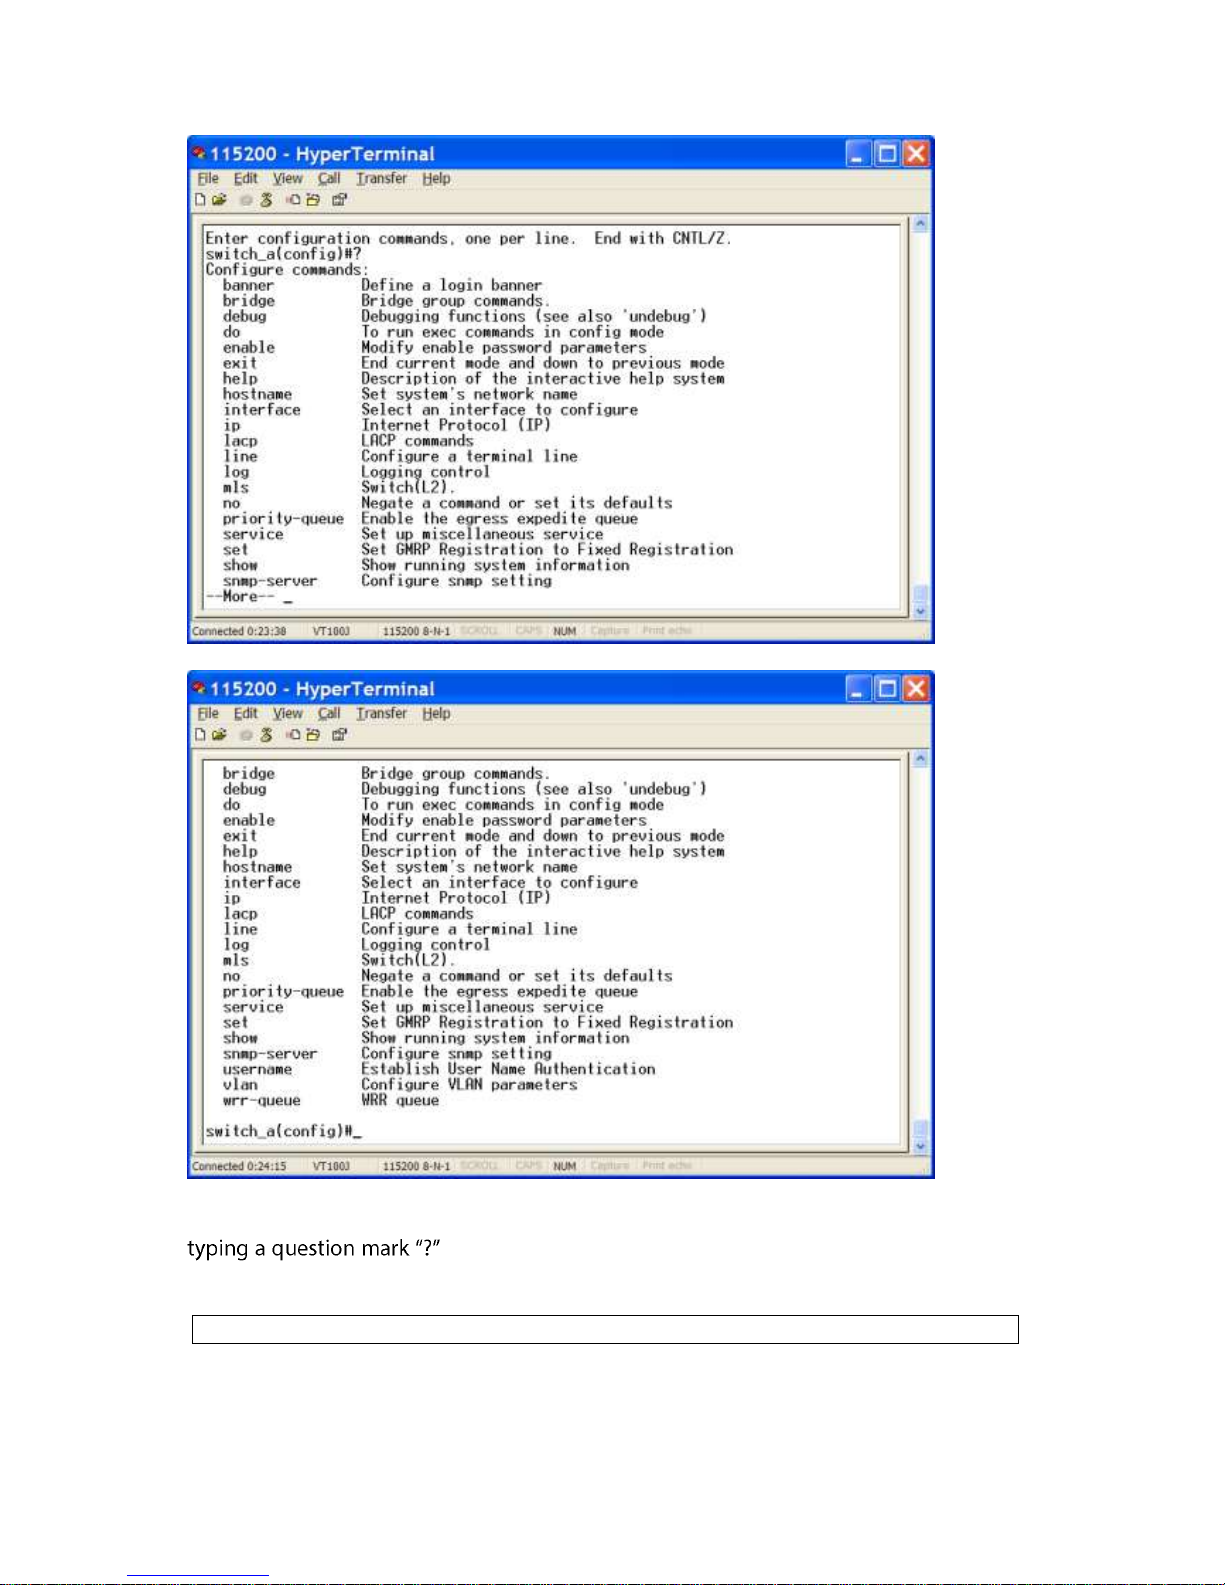
Commands
Configure Mode (or Configure Terminal Mode) serves as a gateway into the modes as
following.
At the switch_a(config)# prompt just press <?> to list the commands.
switch_a(config)#?
Page 86
User Manual Page 86
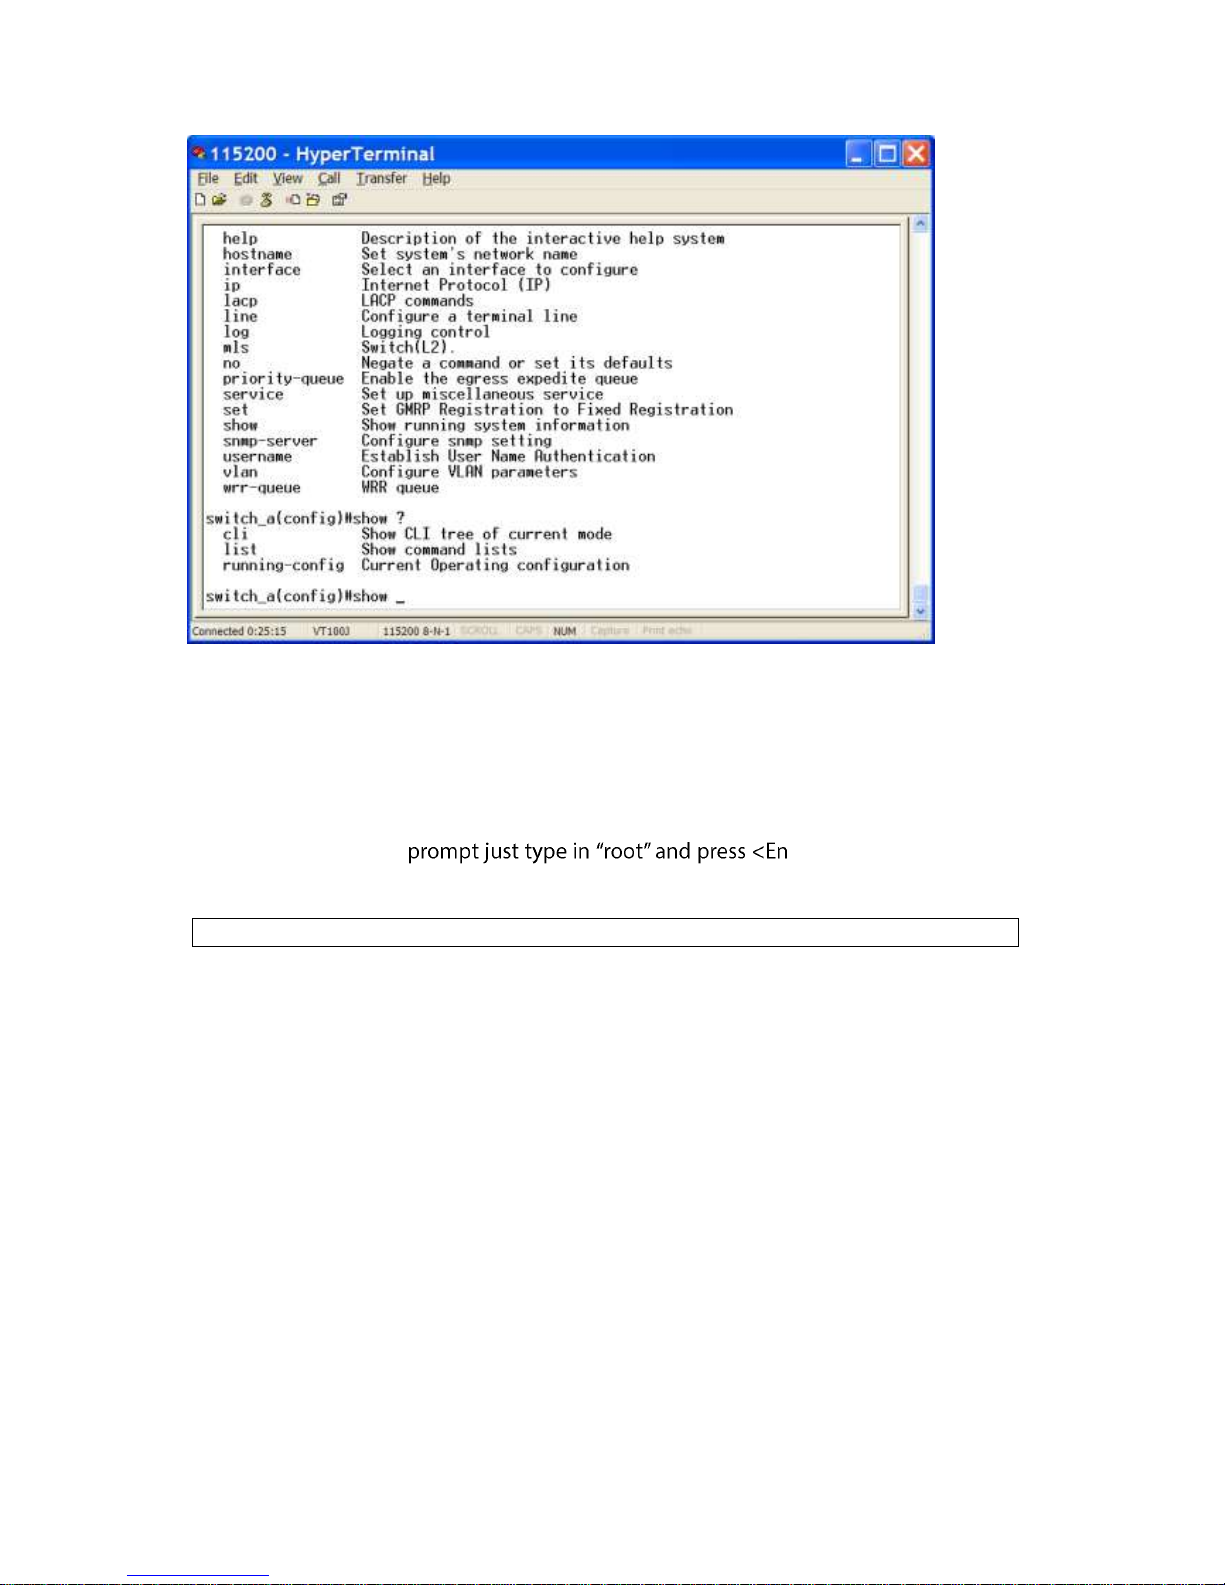
At the switch_a(config)# prompt just type in the full or partial command string then
to display the command keywords or parameters along with a
short description.
switch_a(config)#show ?
Page 87
User Manual Page 87
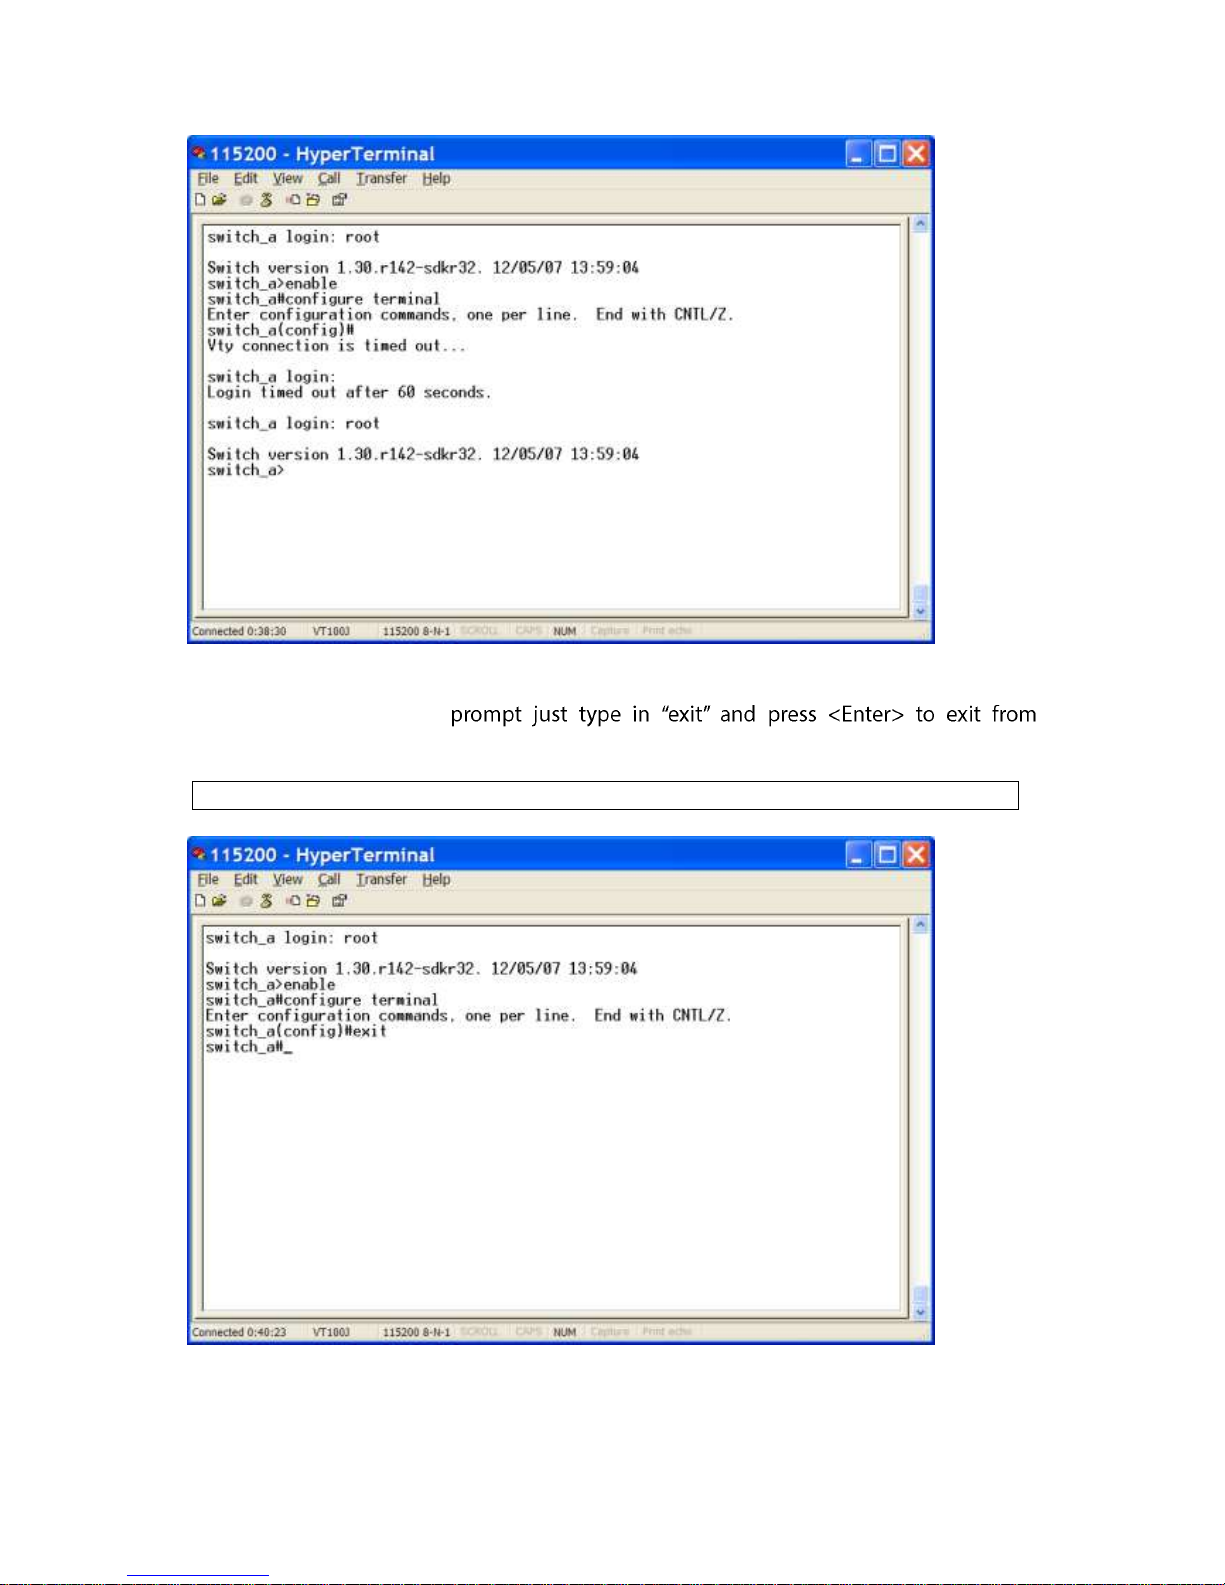
Login timed out
The login session to Configure Mode (or Configure Terminal Mode) has timed out due to
an extended period of inactivity (60 seconds) to indicate authentication attempt timed out.
And the switch_a login: prompt will show on the screen.
Logon back to Exec Mode (View Mode)
At the switch_a login: ter> to logon back to Exec
Mode (or View Mode).
switch_a login: root
Page 88
User Manual Page 88
Exit from Configure Mode (or Configure Terminal Mode)
At the switch_a(config)#
Configure Mode (or Configure Terminal Mode).
switch_a(config)#exit
Page 89
User Manual Page 89
System
System Information, System Name/Password, IP Address, Save Configuration, Firmware
Upgrade, Reboot, Logout
System Name/Password
System Name:
1. Command Mode: Configure mode
Logon to Configure Mode (Configure Terminal Mode).
The switch_a(config)# prompt will show on the screen.
switch_a(config)#
2. Usage:
Use hostname command to set or change the network server name.
Use the no hostname command to disable this function.
3. Command Syntax:
(no) hostname HOSTNAME
HOSTNAME specifies the network name of the system.
4. Example:
The following example sets the hostname to switch, and shows the change in the prompt:
switch_a(config)#hostname switch
switch(config)#
Password:
1. Command Mode: Configure mode
Logon to Configure Mode (Configure Terminal Mode).
The switch_a(config)# prompt will show on the screen.
switch_a(config)#
2. Usage:
Use enable password command to modify or create a password to be used when
entering the Enable mode.
3. Command Syntax:
enable password PASSWORD
PASSWORD specifies the new password of the system.
4. Example:
The following example sets the new password mypasswd to switch:
switch_a(config)#enable password mypasswd
switch_a(config)#
Page 90
User Manual Page 90
IP Address
IP Address/IP Subnet Mask:
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
vlan1.1 means vlan 1.
The switch_a(config-if)# prompt will show on the screen.
switch_a(config)#interface vlan1.1
switch_a(config-if)#
2. Usage:
Use ip address command to set the IP address of an interface.
Use the no ip address command to remove the IP address from an interface.
3. Command Syntax:
ip address IP-ADDRESS
no ip address IP-ADDRESS
no ip address
IP-ADDRESS A.B.C.D/M specifies the IP address and prefix length of an interface.
M specifies IP subnet mask, 8: 255.0.0.0, 16:255.255.0.0, 24: 255.255.255.0.
4. Example:
The following example sets the new IP address 192.168.1.10 and new IP subnet mask
255.255.255.0 to switch:
switch_a(config)#interface vlan1.1
switch_a(config-if)#ip address 192.168.1.10/24
switch_a(config-if)#
Default Gateway:
1. Command Mode: Configure mode
Logon to Configure Mode (Configure Terminal Mode).
The switch_a(config)# prompt will show on the screen.
switch_a(config)#
2. Usage:
Use ip default-gateway command to set the IP address of the default gateway.
Use the no ip default-gateway command to remove the IP address of the default
gateway.
3. Command Syntax:
ip default-gateway IP-ADDRESS
no ip default-gateway
IP-ADDRESS A.B.C.D specifies the IP address of the default gateway.
4. Example:
Page 91
User Manual Page 91
The following example sets the default gateway 192.168.1.254 to switch:
switch_a(config)#ip default-gateway 192.168.1.254
switch_a(config)#
Save Configuration
Load config from TFTP server:
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Use install image command to load configuration file from tftp server to switch.
3. Command Syntax:
install image IP-ADDRESS WORD
IP-ADDRESS specifies the IP address of tftp server.
WORD specifies the file name to be loaded to switch.
4. Example:
The following example specifies upgrading firmware (file name: flash.tgz) from tftp server
(IP address: 192.168.1.100) to switch:
switch_a#install image 192.168.1.100 flash.tgz
switch_a#
Load config to TFTP server:
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Use write config-file command to backup configuration file to tftp server.
3. Command Syntax:
write config-file IP-ADDRESS
IP-ADDRESS specifies the IP address of tftp server.
4. Example:
The following example backups configuration file to tftp server (IP address: 192.168.1.20):
switch_a#write config-file 192.168.1.20
switch_a#
Page 92
User Manual Page 92
Save Configuration:
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Use copy running-config startup-config command to write configurations to the file to
be used at startup. This is the same as the write memory command.
3. Command Syntax:
copy running-config startup-config
4. Example:
The following example specifies writing configurations to the file to be used at startup to
switch:
switch_a#copy running-config startup-config
switch_a#
Restore Default:
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Use restore default command to restore default setting of the switch.
3. Command Syntax:
restore default
4. Example:
The following example restores default setting of the switch:
switch_a#restore default
switch_a#
Auto Save:
1. Command Mode: Configure mode
Logon to Configure Mode (Configure Terminal Mode).
The switch_a(config)# prompt will show on the screen.
switch_a(config)#
Page 93
User Manual Page 93
2. Usage:
Use this command to enable auto save configuration function. The configuration will be
automatically saved at every configured interval while this command is enabled. Use the
no form of this command to disable this feature.
3. Command Syntax:
service auto-config enable
no service auto-config enable
4. Example:
The following example enables or disables auto save configuration to switch:
switch_a(config)#service auto-config enable
switch_a(config)#no service auto-config enable
switch_a(config)#
Auto Save Interval (5~65536 sec):
1. Command Mode: Configure mode
Logon to Configure Mode (Configure Terminal Mode).
The switch_a(config)# prompt will show on the screen.
switch_a(config)#
2. Usage:
Use this command to set the interval when the configuration would be automatically
saved. The range of interval value is from 5 to 65535. And the default value is 30 seconds.
3. Command Syntax:
service auto-config interval WORD
WORD specifies the interval value.
4. Example:
The following example sets the interval WORD (10) when the configuration would be
automatically saved to switch:
switch_a(config)#service auto-config interval 10
switch_a(config)#
Firmware Upgrade
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Page 94
User Manual Page 94
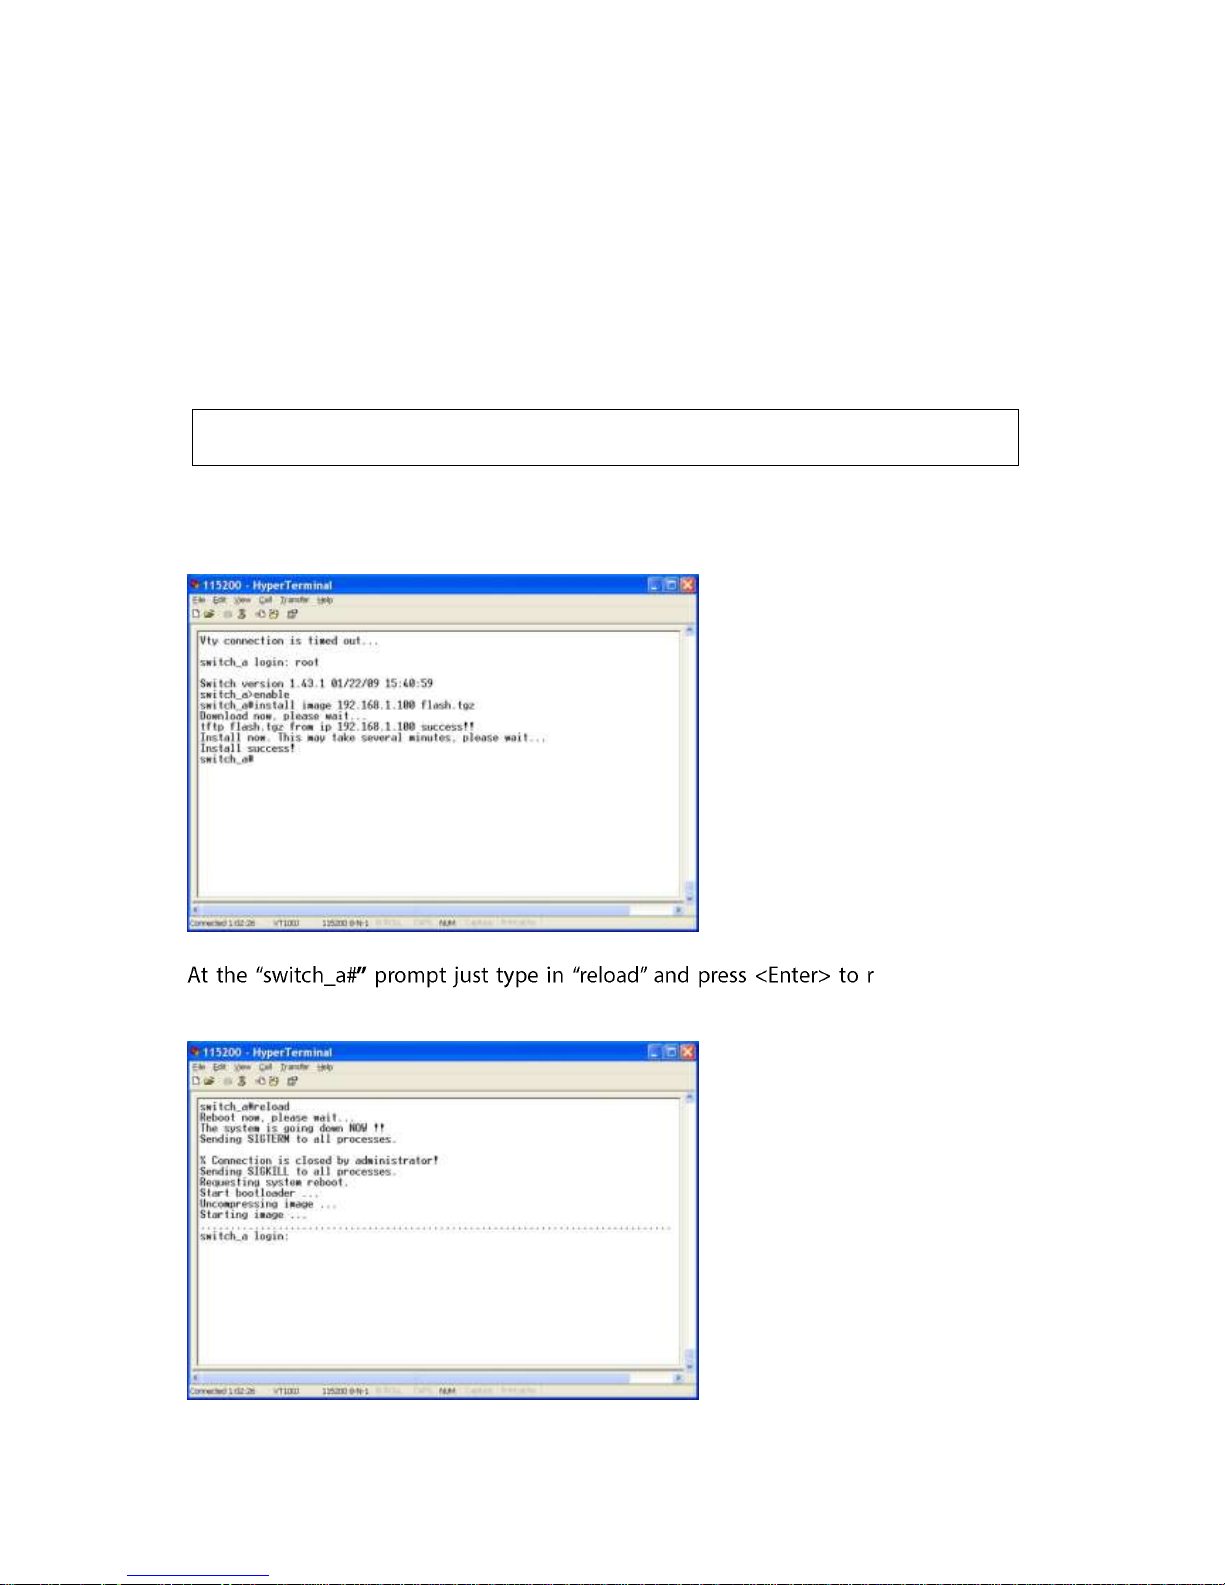
Use install image command to upgrade firmware from tftp server to switch.
3. Command Syntax:
install image IP-ADDRESS WORD
IP-ADDRESS specifies the IP address of tftp server.
WORD specifies the file name to be upgraded to switch.
4. Example:
The following example specifies upgrading firmware (file name: flash.tgz) from tftp server
(IP address: 192.168.1.100) to switch:
switch_a#install image 192.168.1.100 flash.tgz
switch_a#
Please follow the message on the screen during the firmware upgrade process. Do not
turn off the power or perform other functions during this period of time.
eboot the switch
after completing the upgrade process.
Page 95
User Manual Page 95
Reboot
1. Command Mode: Privileged Exec mode
Logon to Privileged Exec Mode (Enable Mode).
The switch_a# prompt will show on the screen.
switch_a#
2. Usage:
Use reload command to restart switch.
3. Command Syntax:
reload
4. Example:
The following example specifies restarting switch:
switch_a#reload
switch_a login:
Logout
1. Command Mode: Exec mode or Privileged Exec mode
Logon to Exec Mode (View Mode) or Privileged Exec Mode (Enable Mode).
The switch_a> or switch_a# prompt will show on the screen.
switch_a>
switch_a#
2. Usage:
Use logout command to exit from the Exec mode or Privileged Exec mode.
3. Command Syntax:
logout
4. Example:
The following example specifies to exit from the Exec mode or Privileged Exec mode.
switch_a>logout
switch_a login:
Page 96
User Manual Page 96
Port
Configuration, Port Status, Rate Control, RMON Statistics, Per Port Vlan Activities
Configuration
Admin Setting:
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
fe1 means port 1.
The switch_a(config-if)# prompt will show on the screen.
switch_a(config)#interface fe1
switch_a(config-if)#
2. Usage:
Use the shutdown command to shut down the selected interface.
Use the no shutdown to disable this function.
3. Command Syntax:
(no) shutdown
4. Example:
The following example shows the use of the shutdown command to shut down the
interface fe1 (port 1):
switch_a(config)#interface fe1
switch_a(config-if)#shutdown
switch_a(config-if)#
Bandwidth:
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
fe1 means port 1.
The switch_a(config-if)# prompt will show on the screen.
switch_a(config)#interface fe1
switch_a(config-if)#
2. Usage:
Use this command to specify the bandwidth for each interface. The bandwidth value is in
bits.
Use the no parameter with this command to remove the bandwidth for each interface.
3. Command Syntax:
Bandwidth BANDWIDTH
no bandwidth
Page 97
User Manual Page 97
BANDWIDTH
<1-10000000000 bits> (usable units: k, m, g)
<1-999>k|m for 1 to 999 kilo bits or mega bits.
1g for 1 giga bits.
4. Example:
The following example shows the use of bandwidth BANDWIDTH (10 mega bits) to the
interface fe1 (port 1):
switch_a(config)#interface fe1
switch_a(config-if)#bandwidth 10m
switch_a(config-if)#
Duplex:
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
fe1 means port 1.
The switch_a(config-if)# prompt will show on the screen.
switch_a(config)#interface fe1
switch_a(config-if)#
2. Usage:
Use duplex command to specify the duplex mode to be used for each interface.
Use the no duplex to disable this function.
3. Command Syntax:
(no) duplex MODE
MODE specifies the duplex mode: auto, full, half.
4. Example:
The following example shows the use of duplex MODE (full) to the interface fe1 (port 1):
switch_a(config)#interface fe1
switch_a(config-if)#duplex full
switch_a(config-if)#
Flow control:
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
fe1 means port 1.
The switch_a(config-if)# prompt will show on the screen.
switch_a(config)#interface fe1
switch_a(config-if)#
Page 98
User Manual Page 98
2. Usage:
Use flowcontrol on command to enable flow control, and configure the flow control
mode for the port.
Use the no flowcontrol to disable this function.
3. Command Syntax:
flowcontrol on
no flowcontrol
4. Example:
The following example shows the use of flowcontrol on to the interface fe1 (port 1):
switch_a(config)#interface fe1
switch_a(config-if)#flowcontrol on
switch_a(config-if)#
Port Status
1. Command Mode: Exec mode or Privileged Exec mode
Logon to Exec Mode (View Mode) or Privileged Exec Mode (Enable Mode).
The switch_a> or switch_a# prompt will show on the screen.
switch_a>
switch_a#
2. Usage:
Use the show interface command to display interface configuration and status.
3. Command Syntax:
show interface IFNAME
IFNAME specifies the name of the interface for which status and configuration
information is desired.
4. Example:
The following example shows the use of show interface to display interface configuration
and status of the interface fe1 (port 1):
switch_a>show interface fe1
Rate Control
1. Command Mode: Interface mode
Logon to Configure Mode (Configure Terminal Mode).
Then logon to Interface mode.
fe1 means port 1.
The switch_a(config-if)# prompt will show on the screen.
Page 99
User Manual Page 99
switch_a(config)#interface fe1
switch_a(config-if)#
2. Usage:
Use this command to specify the ingress/egress rate to be used for each interface. The
bandwidth value is in bits.
Use the no parameter with this command to remove the ingress/egress rate to be used for
each interface.
3. Command Syntax:
(no) rate-control ingress/egress VALUE
VALUE
<1-10000000000 bits> (usable units: k, m, g)
<1-999>k|m for 1 to 999 kilo bits or mega bits.
1g for 1 giga bits.
4. Example:
The following example shows the use of rate-control ingress VALUE (10 mega bits) to the
interface fe1 (port 1):
switch_a(config)#interface fe1
switch_a(config-if)#rate-control ingress 10m
switch_a(config-if)#
RMON Statistics
1. Command Mode: Exec mode or Privileged Exec mode
Logon to Exec Mode (View Mode) or Privileged Exec Mode (Enable Mode).
The switch_a> or switch_a# prompt will show on the screen.
switch_a>
switch_a#
2. Usage:
Use the show interface statistics command to display RMON statistics of interface.
3. Command Syntax:
show interface statistics IFNAME
IFNAME specifies the name of the interface for which RMON statistics is desired.
4. Example:
The following example shows the use of show interface statistics to display RMON
statistics of the interface fe1 (port 1):
switch_a>show interface statistics fe1
Page 100
User Manual Page 100
Per Port Vlan Activities
1. Command Mode: Exec mode or Privileged Exec mode
Logon to Exec Mode (View Mode) or Privileged Exec Mode (Enable Mode).
The switch_a> or switch_a# prompt will show on the screen.
switch_a>
switch_a#
2. Usage:
Use show vlan command to display information about a particular VLAN by specifying the
VLAN ID.
3. Command Syntax:
show vlan <2-4094>
<2-4094> VLAN ID.
4. Example:
The following is an output of show vlan command displaying information about VLAN 2:
switch_a>show vlan 2
 Loading...