

Page 1
SSG320M AND
SSG350M SECURE
SERVICES
GATEWAYS
DATASHEET
Product Overview
The Juniper Networks SSG300 line
consists of purpose-built security
appliances that deliver the ideal
blend of performance, security,
routing, and LAN/WAN connectivity
for large, regional branch offices and
medium-size, standalone businesses.
Traffic flowing in and out of a regional
office or business is protected
from worms, spyware, trojans, and
malware by a complete set of Unified
Threat Management security features,
including stateful firewall, IPsec VPN,
intrusion prevention system (IPS),
antivirus (includes antispyware,
antiadware, antiphishing), antispam,
and Web filtering. The SSG300 line
comprises the SSG350M and the
SSG320M Secure Services Gateways.
Product Description
The Juniper Networks® SSG300 line of secure services gateways comprises highperformance security platforms that help businesses stop internal and external attacks,
prevent unauthorized access, and achieve regulatory compliance. The Juniper Networks
SSG350M Secure Services Gateway provides 500 Mbps of stateful firewall performance
and 225 Mbps of IPsec VPN performance, while the Juniper Networks SSG320M Secure
Services Gateway provides 400 Mbps of stateful firewall performance and 175 Mbps of
IPsec VPN performance.
These products focus on three key disciplines:
Security: Protection against worms, viruses, trojans, spam, and emerging malware
is delivered by proven Unified Threat Management (UTM) security features that are
backed by best-in-class partners. To address internal security requirements and facilitate
regulatory compliance, the SSG300 line supports an advanced set of network protection
features such as security zones, virtual routers, and VLANs that allow administrators to
divide the network into distinct, secure domains, each with their own unique security
policy. Policies protecting each security zone can include access control rules and
inspection by any of the supported UTM security features.
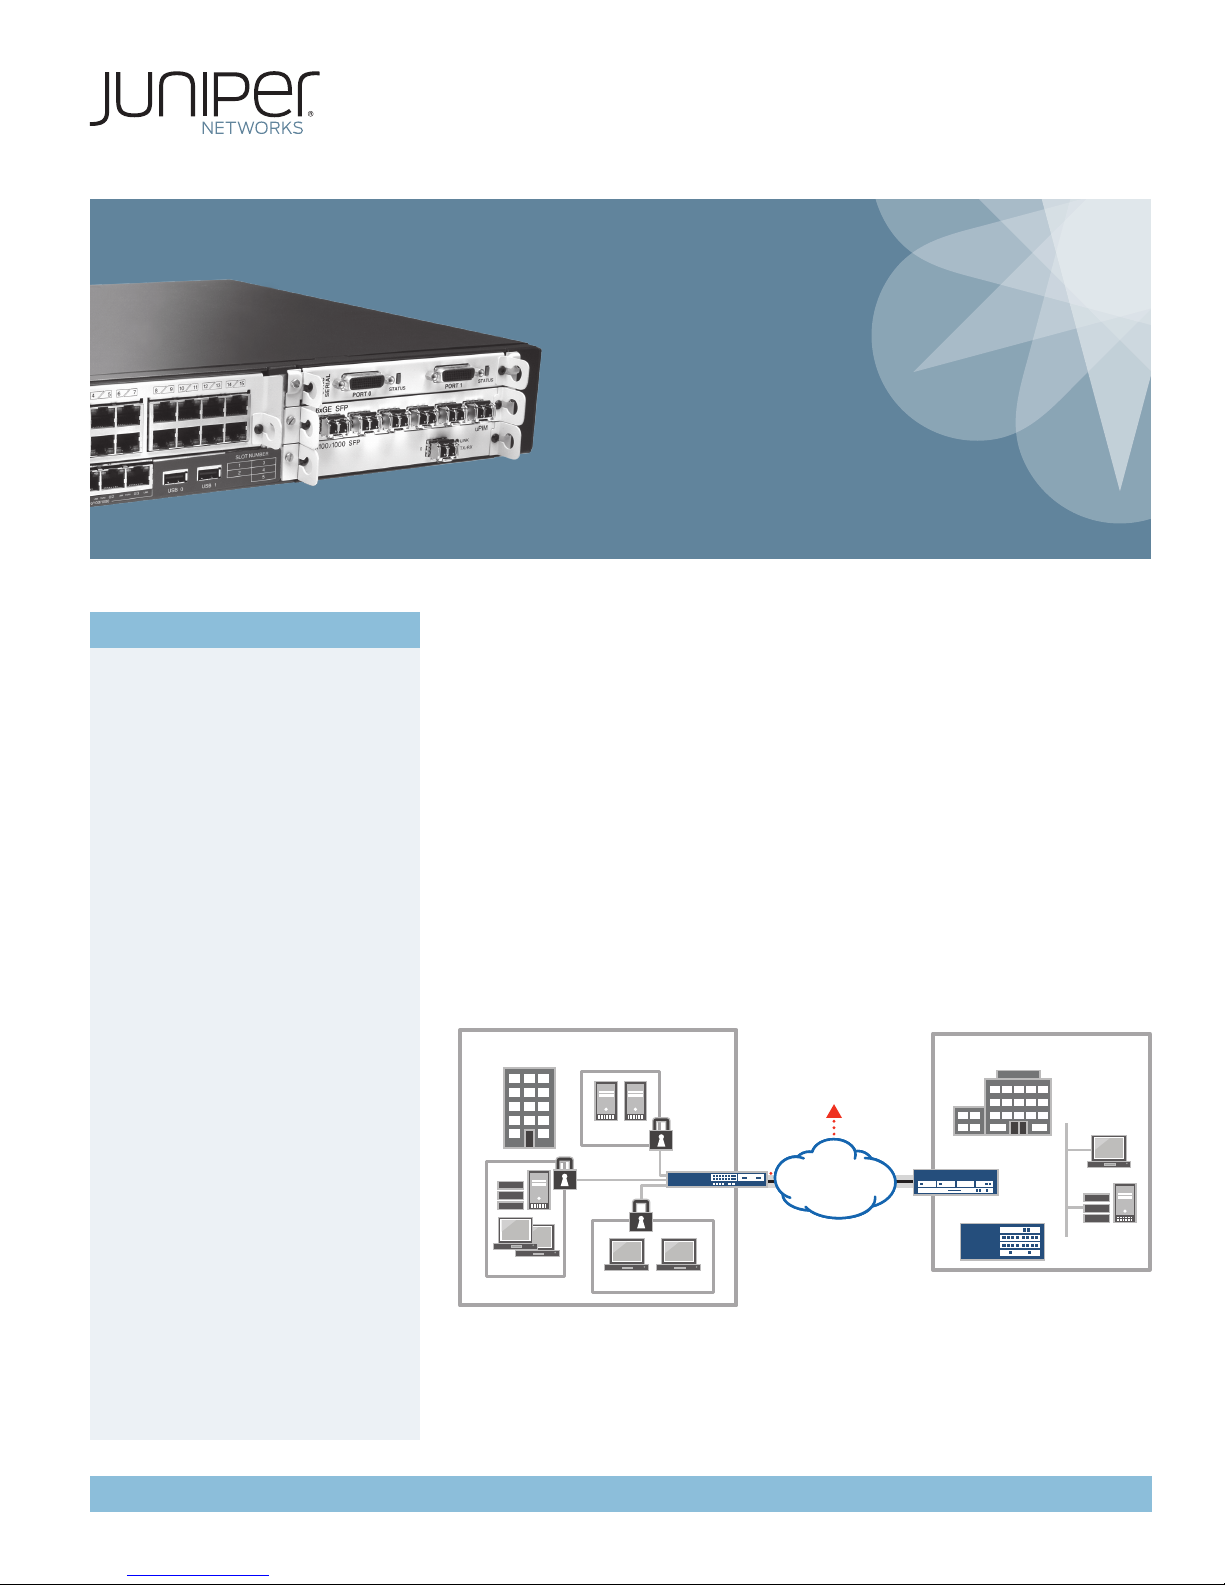
Regional Oce
Zone A
SSG350M
Internet
Headquarters
M7i
NetScreen-5400
Zone C
The SSG350M deployed at a branch oce for secure Internet connectivity and site-to-site
VPN to corporate headquarters. Internal branch oce resources are protected with unique
Zone B
security policies applied to each security zone.
1
Page 2
Connectivity and Routing: The SSG300 line provides four onboard
10/100/1000 interfaces complemented by I/O expansion slots that
can house a mix of LAN or WAN interfaces, making the SSG300
line an extremely flexible platform. The broad array of I/O options
coupled with WAN protocol and encapsulation support makes the
SSG300 line of gateways easily deployable as traditional branch
oce routers or as consolidated security and routing devices, which
can help reduce CapEx and OpEx.
Access Control Enforcement: The SSG300 line of gateways can act
as enforcement points in a Juniper Networks Unified Access Control
deployment with the simple addition of the Juniper Networks IC
management engine by interacting with the SSG300 line to augment
or replace the firewall-based access control. It grants/denies access
based on more granular criteria, including endpoint state and user
identity in order to accommodate the dramatic shis in attack
landscape and user characteristics.
In addition, Juniper Networks Professional Services will collaborate
with your team to identify goals, define the deployment process,
create or validate the network design, and manage the deployment
to its successful conclusion. Whether it involves simple lab testing
or a major network implementation, Juniper Networks Professional
Services is there to help you ensure success.
Series UAC Appliances. The IC Series functions as a central policy
Features and Benefits
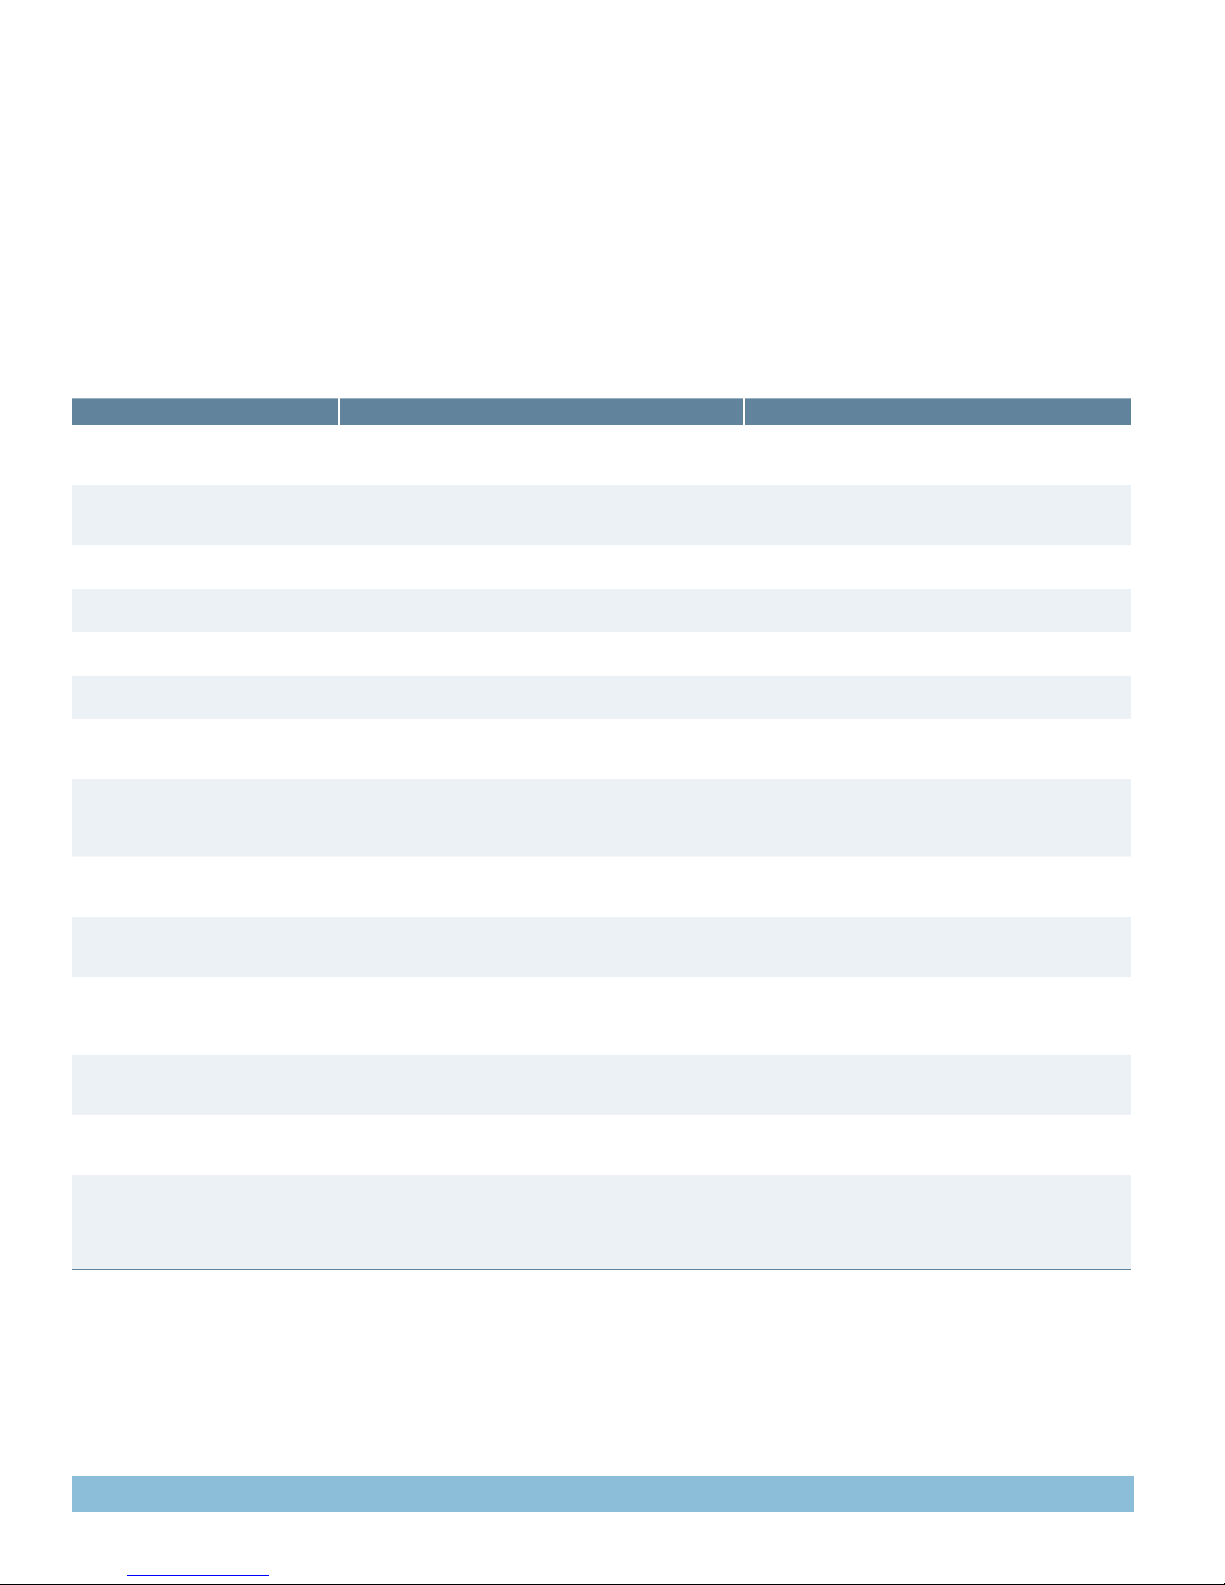
Feature Feature Description Benefit
High performance Purpose-built platform is assembled from custom-built
Best-in-class UTM security features UTM security features (antivirus, antispam, Web
Integrated antivirus Annually licensed antivirus engine, provided by Juniper,
Integrated antispam Annually licensed antispam oering, provided by
Integrated Web filtering Annually licensed Web filtering solution, provided by
Integrated intrusion prevention
system (IPS) (Deep Inspection)
Fixed Interfaces Four fixed 10/100/1000 interfaces, two USB ports, one
Network segmentation Bridge groups, security zones, virtual LANs and virtual
Interface modularity Six interface expansion slots support optional T1, E1,
Robust routing engine Proven routing engine supports OSPF, BGP and RIP v1/2
Juniper Networks Unified Access
Control enforcement point
Management flexibility Use any one of three mechanisms, CLI, WebUI or Juniper
Auto-Connect VPN Automatically sets up and takes down VPN tunnels
World-class professional services From simple lab testing to major network
hardware, powerful processing and a security-specific
operating system.
filtering, IPS) stop all manner of viruses and malware
before they damage the network.
is based on Kaspersky Lab engine.
Juniper, is based on Sophos technology.
Juniper, is based on Websense SurfControl technology.
Annually licensed IPS engine is available with Juniper
Networks Deep Inspection Firewall Signature Packs.
console port and one auxiliary port are standard on all
SSG300 line models.
routers allow administrators to deploy security policies
to isolate guests, wireless networks and regional servers
or databases.*
Serial, ADSL/ADSL2/ADSL2+, G.SHDSL, 10/100/1000,
and SFP connectivity.
along with Frame Relay, Multilink Frame Relay, PPP,
Multilink PPP and HDLC.
Interacts with the centralized policy management
engine (IC Series) to enforce session-specific access
control policies using criteria such as user identity,
device security state and network location.
Networks Network and Security Manager (NSM), to
securely deploy, monitor and manage security policies.
between spoke sites in a hub-and-spoke topology.
implementations, Juniper Networks Professional
Services will collaborate with your team to identify
goals, define the deployment process, create or validate
the network design and manage the deployment.
Delivers performance headroom required to protect
against internal and external attacks now and into
the future.
Ensures that the network is protected against all
manner of attacks.
Stops viruses, spyware, adware and other malware.
Blocks unwanted email from known spammers and
phishers.
Controls/blocks access to malicious Web sites.
Prevents application-level attacks from flooding the
network.
Provides high-speed LAN connectivity, future
connectivity and flexible management.
Powerful capabilities facilitate deploying security for
various internal, external and DMZ sub-groups on the
network, to prevent unauthorized access.
Delivers combination of LAN and WAN connectivity
on top of unmatched security to reduce costs and
extend investment protection.
Enables the deployment of consolidated security
and routing device, thereby lowering operational and
capital expenditures.
Improves security posture in a cost-eective
manner by leveraging existing customer network
infrastructure components and best-in-class
technology.
Enables management access from any location,
eliminating on-site visits thereby improving response
time and reducing operational costs.
Provides a scalable VPN solution for mesh
architectures with support for latency-sensitive
applications such as VoIP and video conferencing.
Transforms the network infrastructure to ensure that
it is secure, flexible, scalable and reliable.
*Bridge groups supported only on uPIMs in Juniper Networks ScreenOS® Software 6.0 and higher releases.
2
Page 3
Product Options
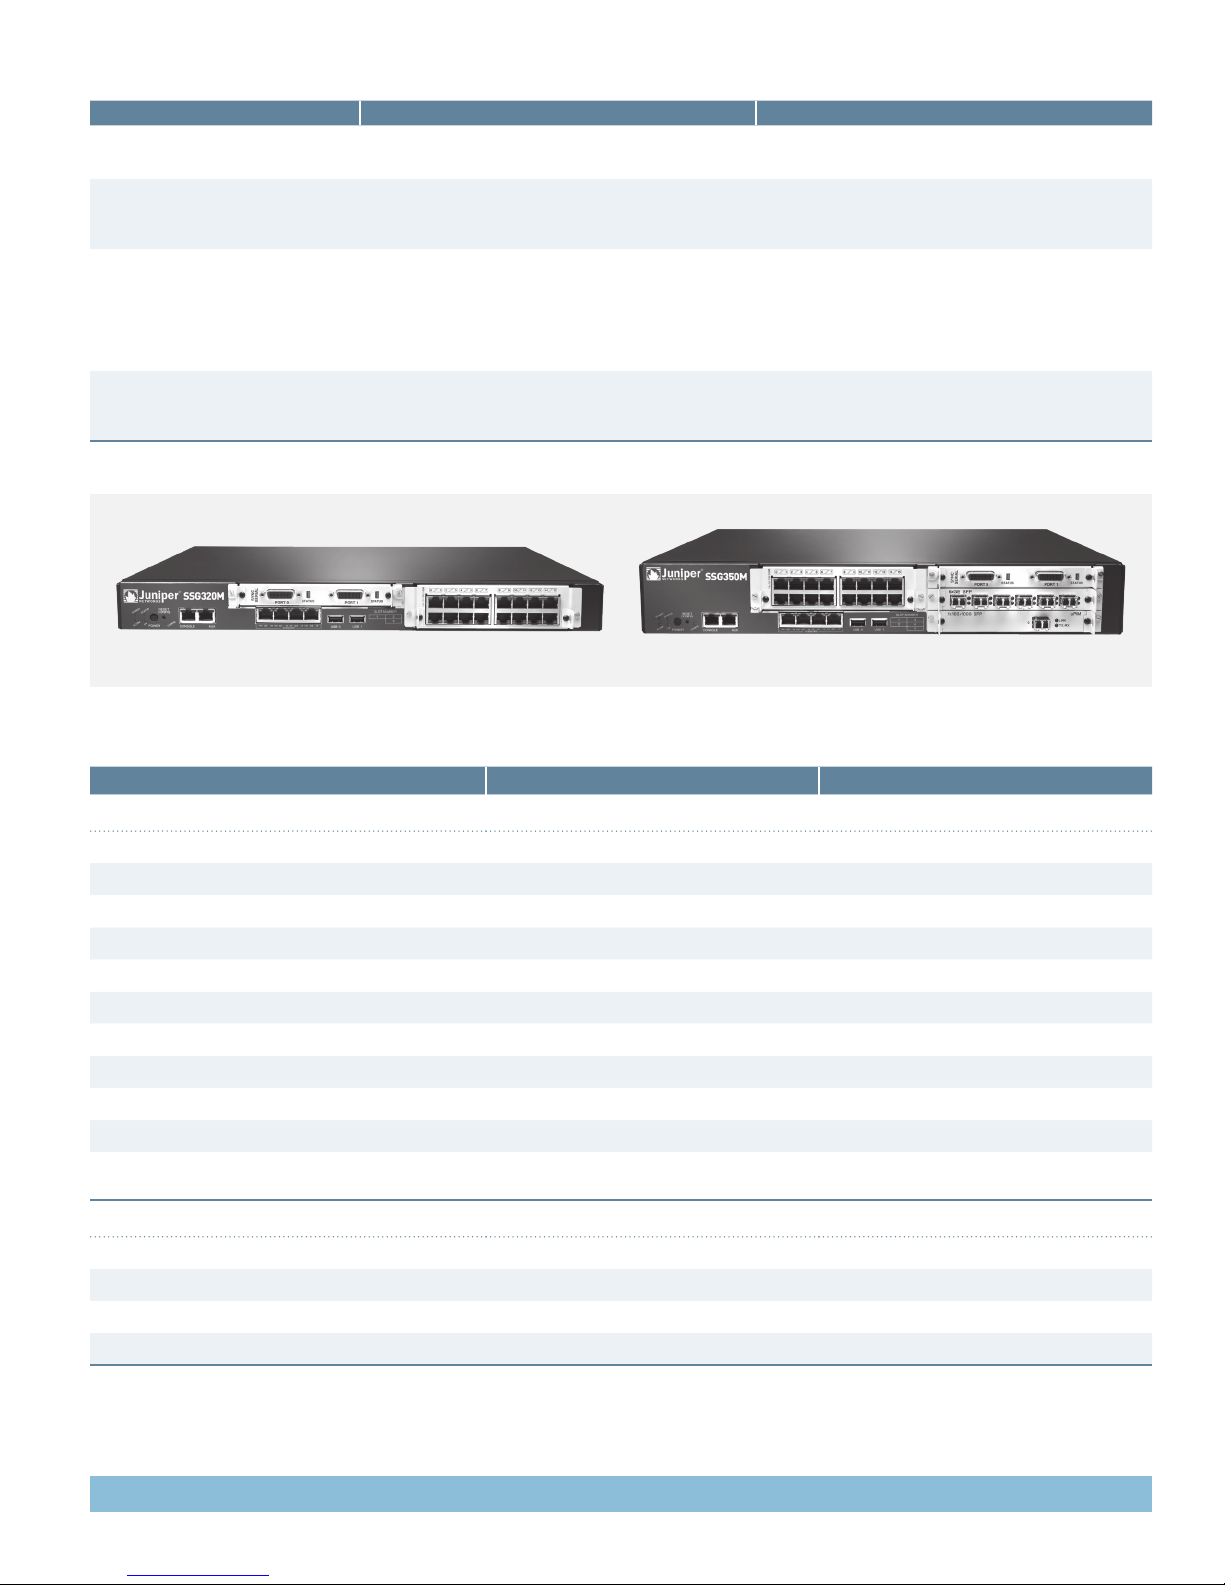
Option Option Description Applicable Products
Network Equipment Building
Systems (NEBS) compliance
NEBS-compliant versions of the SSG350M are
available.
SSG350M
DRAM All models in the SSG300 line are available with
UTM/Content Security (high
memory option required)
I/O options Three (SSG320M) or five (SSG350M) expansion slots
1 GB of DRAM. The SSG320M and SSG350M are also
available in 256 MB-DRAM versions.
With the addition of licensing keys, the SSG300
line can be configured with any combination of the
following best-in-class UTM and content security
functionality: antivirus (includes antispyware,
antiphishing), IPS (Deep Inspection firewall), Web
filtering and/or antispam.
support optional T1, E1, Serial, ADSL2+, G.SHDSL,
10/100/1000, and SFP.
SSG320M
SSG350M
SSG320M
SSG350M high-memory model only
SSG320M high-memory model only
SSG350M
SSG320M
SSG350M
Specifications
SSG320M SSG350M
Maximum Performance and Capacity
ScreenOS version tested ScreenOS 6.3 ScreenOS 6.3
Firewall performance (Large packets) 450+ Mbps 550+ Mbps
Firewall performance (IMIX)
Firewall Packets Per Second (64 byte) 175,000 PPS 225,000 PPS
AES256+SHA-1 VPN performance 175 Mbps 225 Mbps
3DES+SHA-1 VPN performance 175 Mbps 225 Mbps
Maximum concurrent sessions 64,000 128,000
New sessions/second 10,000 12,500
Maximum security policies 2,000 2,000
Maximum users supported Unrestricted Unrestricted
Convertible to Juniper Networks Junos
system 8.0 or higher
(2)
®
operating
(1)
400 Mbps 500 Mbps
Yes Yes
Network Connectivity
Fixed I/O 4x10/100/1000 4x10/100/1000
Physical Interface Module (PIM) Slots 3 5
WAN interface options (PIMS) Serial, T1, E1, ADSL/ADSL2/ADSL2+, G.SHDSL Serial, T1, E1, ADSL/ADSL2/ADSL2+, G.SHDSL
LAN interface options (uPIMS) 8x10/100/1000, 16x10/100/1000, and 6xSFP 8x10/100/1000, 16x10/100/1000, and 6xSFP
3
Page 4

Specifications (continued)
SSG320M SSG350M
Firewall
Network attack detection Yes Yes
DoS and DDoS protection Yes Yes
TCP reassembly for fragmented packet protection Yes Yes
Brute force attack mitigation Yes Yes
SYN cookie protection Yes Yes
Zone-based IP spoofing Yes Ye s
Malformed packet protection Yes Yes
Unified Threat Management
IPS (Deep Inspection firewall) Ye s Yes
Protocol anomaly detection Yes Ye s
Stateful protocol signatures Yes Ye s
IPS/DI attack pattern obfuscation Yes Yes
Antivirus Yes Yes
Signature database 200,000+ 200,000+
Protocols scanned POP3, HTTP, SMTP, IMAP, FTP, IM POP3, HTTP, SMTP, IMAP, FTP, IM
Antispyware Yes Yes
Antiadware Yes Yes
Anti-keylogger Ye s Yes
Instant message AV Yes Yes
Antispam Yes Ye s
Integrated URL filtering Yes Yes
External URL filtering
(4)
VoIP Security
H.323 ALG Yes Yes
SIP ALG Ye s Ye s
MGCP ALG Yes Ye s
SCCP ALG Yes Ye s
NAT for VoIP protocols Ye s Ye s
IPsec VPN
Concurrent VPN tunnels 500 500
Tunnel interfaces 100 300
DES (56-bit), 3DES (168-bit) and AES (256-bit) Yes Yes
MD-5 and SHA-1 authentication Yes Yes
Manual key, IKE, IKEv2 with EAP, PKI (X.509) Yes Yes
Perfect forward secrecy (DH Groups) 1,2,5 1,2,5
Prevent replay attack Ye s Yes
Remote access VPN Yes Yes
L2TP within IPsec Yes Yes
IPsec NAT traversal Yes Yes
Auto-Connect VPN Ye s Yes
Redundant VPN gateways Yes Yes
User Authentication and Access Control
Built-in (internal) database - user limit 500 500
Third-party user authentication RADIUS, RSA SecureID, LDAP RADIUS, RSA SecureID, LDAP
RADIUS Accounting Yes – start/stop Yes – start/stop
XAUTH VPN authentication Yes Yes
Web-based authentication Yes Yes
802.1X authentication Ye s Ye s
Unified Access Control enforcement point Yes Yes
(3)
Yes Yes
4
Page 5

Specifications (continued)
SSG320M SSG350M
PKI Support
PKI Certificate requests (PKCS 7 and PKCS 10) Yes Yes
Automated certificate enrollment (SCEP) Ye s Yes
Online Certificate Status Protocol (OCSP) Yes Yes
Certificate Authorities supported VeriSign, Entrust, Microso, RSA Keon, iPlanet
Self-signed certificates Ye s Yes
(Netscape) Baltimore, DoD PKI
Virtualization
Maximum number of security zones 40 40
Maximum number of virtual routers 8 8
Bridge groups* Yes Yes
Maximum number of VLANs 125 125
Routing
BGP instances 8 8
BGP peers 36 48
BGP routes 10,000 10,000
OSPF instances 3 3
OSPF routes 10,000 10,000
RIP v1/v2 instances 128 128
RIP v2 routes 10,000 10,000
Static routes 10,000 10,000
Source-based routing Ye s Ye s
Policy-based routing Ye s Ye s
ECMP Yes Yes
Multicast Yes Yes
Reverse Path Forwarding (RPF) Yes Yes
IGMP (v1, v2) Ye s Ye s
IGMP Proxy Ye s Ye s
PIM SM Yes Yes
PIM SSM Yes Ye s
Multicast inside IPsec tunnel Yes Ye s
Encapsulations
PPP Yes Yes
MLPPP Yes Yes
MLPP max physical interfaces 6 10
Frame Relay Ye s Ye s
MLFR (FRF .15, FRF .16) Ye s Ye s
MLFR max physical interfaces 6 10
HDLC Yes Yes
IPv6
Dual stack IPv4/IPv6 firewall and VPN Ye s Ye s
IPv4 to/from IPv6 translations and encapsulations Yes Yes
Syn-Cookie and Syn-Proxy DoS Attack Detection Yes Yes
SIP, RTSP, Sun-RPC, and MS-RPC ALG’s Yes Yes
RIPng Ye s Ye s
BGP Yes Ye s
Transparent mode Yes Yes
NSRP Ye s Ye s
DHCPv6 Relay Yes Ye s
Mode of Operation
Layer 2 (transparent) mode
Layer 3 (route and/or NAT) mode Yes Yes
*Bridge groups supported only on uPIMs in ScreenOS 6.0 and higher releases.
(5)
Yes Yes
VeriSign, Entrust, Microso, RSA Keon, iPlanet
(Netscape) Baltimore, DoD PKI
5
Page 6

Specifications (continued)
SSG320M SSG350M
Address Translation
Network Address Translation (NAT) Yes Yes
Port Address Translation (PAT) Yes Ye s
Policy-based NAT/PAT (L2 and L3 mode) Yes Yes
Mapped IP (L3 mode) 4,000 4,000
Virtual IP (L3 mode) 32 32
MIP/VIP Grouping (L3 mode) Ye s Ye s
IP Address Assignment
Static Ye s Ye s
DHCP, PPPoE client Ye s Ye s
Internal DHCP server Ye s Yes
DHCP relay Yes Ye s
Trac Management Quality of Service (QoS)
Guaranteed bandwidth Yes - per policy Yes - per policy
Maximum bandwidth Yes - per policy Yes - per policy
Ingress trac policing Yes Ye s
Priority-bandwidth utilization Yes Ye s
DiServ marking Yes - per policy Yes - per policy
High Availability (HA)
Active/Active - L3 mode Yes Ye s
Active/Passive - Transparent & L3 mode Ye s Ye s
Configuration synchronization Yes Yes
Session synchronization for firewall and VPN Yes Ye s
VRRP Yes Ye s
Session failover for routing change Yes Yes
Device failure detection Ye s Ye s
Link failure detection Ye s Ye s
Authentication for new HA members Yes Yes
Encryption of HA trac Ye s Ye s
System Management
WebUI (HTTP and HTTPS) Yes Yes
Command line interface (console) Yes Yes
Command line interface (telnet) Ye s Ye s
Command line interface (SSH) Yes v1.5 and v2.0 compatible Yes v1.5 and v2.0 compatible
Network and Security Manager (NSM) Ye s Ye s
All management via VPN tunnel on any interface Ye s Yes
Rapid deployment No No
Administration
Local administrator database size 20 20
External administrator database support RADIUS, RSA SecurID, LDAP RADIUS, RSA SecureID, LDAP
Restricted administrative networks 50 50
Root Admin, Admin and Read Only user levels Yes Yes
Soware upgrades TFTP, WebUI, NSM, SCP, USB TFTP, WebUI, NSM, SCP, USB
Configuration rollback Yes Ye s
Logging/Monitoring
Syslog (multiple servers) Yes - up to 4 servers Yes - up to 4 servers
Email (two addresses) Ye s Ye s
NetIQ WebTrends Yes Ye s
SNMP (v3) Yes Ye s
SNMP full custom MIB Yes Yes
Traceroute Ye s Ye s
VPN tunnel monitor Ye s Ye s
6
Page 7

Specifications (continued)
SSG320M SSG350M
External Flash
Additional log storage USB 1.1 USB 1.1
Event logs and alarms Yes Ye s
System configuration script Yes Yes
ScreenOS Soware Ye s Yes
Dimensions and Power
Dimensions (W x H x D) 17.5 x 1.8 x 15.1 in
Weight 15.0 lb (no interface modules)
Rack mountable Yes, 1 RU Yes, 1.5 RU
Power supply (AC) 100-240 VAC 275 W 300 W
Average power consumption 80 W (No PIMs) 80 W (No PIMs)
Maximum power consumption 320 W 350 W
Input frequency 47-63 Hz 47-63 Hz
Maximum current consumption 100 – 240 VAC, 3.2 A – 1.3 A 100 – 240 VAC, 3.5 A – 1.5 A
Maximum Inrush current 100 – 240 VAC, 42 A – 62 A 100 – 240 VAC, 13 A – 75 A
Average heat dissipation 273 BTU (No PIMs) 273 BTU (No PIMs)
Maximum heat dissipation 1091 BTU 1195 BTU
Power supply (DC) N/A -48 to -60 VDC, 300 watts
Noise level 40.0 dB 59.2 dB
(44.5 x 4.5 x 38.3 cm)
6.8 kg
Certifications
Safety certifications CSA, TUV, CB CSA, TUV, CB
EMC certifications
NEBS No Level 3
MTBF (Bellcore model) 7.2 years 6.8 years
FCC class A, CE class A, C-Tick, VCCI class B FCC class A, CE class A, C-Tick, VCCI class B
Security Certifications
Common Criteria: EAL4 Yes (ScreenOS 6.2) Yes (ScreenOS 6.2)
FIPS 140-2: Level 2 Yes Yes
ICSA Firewall and VPN Yes Ye s
Operating Environment
Operating temperature 32° to 122° F (0° to 50° C) 32° to 122° F (0° to 50° C)
Non-operating temperature -4° to 158° F (-20° to 70° C) -4° to 158° F (-20° to 70° C)
Humidity 10% to 90% noncondensing 10% to 90% noncondensing
(1) Performance, capacity and features listed are based upon systems running ScreenOS 6.3 and are the measured maximums under ideal testing conditions unless otherwise noted. Actual results
may vary based on ScreenOS release and by deployment. For a complete list of supported ScreenOS versions for SSG Series gateways, please visit the Juniper Customer Support Center (www.
juniper.net/customers/support/) and click on ScreenOS Software Downloads.
(2) IMIX stands for Internet mix and is more demanding than a single packet size as it represents a traffic mix that is more typical of a customer’s network. The IMIX traffic used is made up of 58.33%
64 byte packets + 33.33% 570 byte packets + 8.33% 1518 byte packets of UDP traffic.
(3) UTM Security features (IPS/Deep Inspection, antivirus, antispam and Web filtering) are delivered by annual subscriptions purchased separately from Juniper Networks. Annual subscriptions provide
signature updates and associated support. The high memory option is required for UTM security features.
(4) Redirect Web filtering sends traffic from the firewall to a secondary server. The redirect feature is free. However, it does require the purchase of a separate Web filtering license from either Websense
or SurfControl.
(5) NAT, PAT, policy-based NAT, virtual IP, mapped IP, virtual systems, virtual routers, VLANs, OSPF, BGP, RIPv2, Active/Active HA and IP address assignment are not available in Layer 2 transparent mode.
17.5 x 2.6 x 15.1 in
(44.5 x 6.6 x 38.3 cm)
25.0 lb (no interface modules +
one power supply) (11.34 kg)
Juniper Networks Services and Support
Juniper Networks is the leader in performance-enabling services that are designed to accelerate, extend, and optimize your highperformance network. Our services allow you to maximize operational efficiency while reducing costs and minimizing risk, achieving a
faster time to value for your network. Juniper Networks ensures operational excellence by optimizing the network to maintain required
levels of performance, reliability, and availability. For more details, please visit www.juniper.net/us/en/products-services.
7
Page 8

Ordering Information
Model Number Description
SSG320M
SSG-320M-SB SSG320M, ScreenOS, base memory (256 MB),
SSG-320M-SH SSG320M, ScreenOS, base memory (1 GB),
SSG350M
SSG-350M-SB SSG350M, ScreenOS, base memory (256 MB),
SSG-350M-SH SSG350M, ScreenOS, base memory (1 GB),
SSG-350M-SB-TAA SSG350M gateway, ScreenOS, base memory
SSG-350M-SH-TAA SSG350M gateway, ScreenOS, base memory
SSG-350M-SB-DCN-TAA
SSG-350M-SH-DCN-TAA
SSG300 Line I/O Options
JX-2T1-RJ48-S 2-port T1 PIM with integrated CSU/DSU
JX-2E1-RJ48-S 2-port E1 PIM with integrated CSU/DSU
JX-2Serial-S 2-port Synchronous Serial PIM
JX-1ADS L-A-S 1-port ADSL 2/2+ Annex A PIM
JX-1ADSL-B-S 1-port ADSL 2/2+ Annex B PIM
JX-2SHDSL-S 2-port 2-wire or 1-port 4-wire G.SHDSL PIM
JX-1BRI-ST-S 1-port ISDN BRI S/T PIM
JXU-6GE-SFP-S 6-port SFP Gigabit Ethernet Universal PIM2
JXU-8GE-TX-S 8-port Gigabit Ethernet 10/100/1000 Copper
JXU-16GE-TX-S 16-port Gigabit Ethernet 10/100/1000 Copper
JX-SFP-1GE-LX Small form factor pluggable 1000BASE-LX
JX-SFP-1GE-SX Small form factor pluggable 1000BASE-SX
HW security, AC power supply
HW security, AC power supply
HW security, AC power supply
HW security, AC power supply
(256 MB), 5 PIM slots, HW Crypto, AC power
supply, TAA, 19” rack mount
(1 GB), 5 PIM slots, HW Crypto, AC power supply,
TAA, 19” rack mount
SSG350M gateway, ScreenOS, base memory
(256 MB), 5 PIM slots, HW Crypto, DC power
supply, fan filter, NEBS, TAA, 19” rack mount
SSG350M gateway, ScreenOS, base memory
(1 GB), 5 PIM slots, HW Crypto, DC power supply,
fan filter, NEBS, TAA, 19” rack mount
Universal PIM2
Universal PIM2
Gigabit Ethernet Optical Transceiver Module
Gigabit Ethernet Optical Transceiver Module
Model Number Description
Unified Threat Management/Content Security
(High Memory Option Required)
NS-K-AVS-SSG350
NS-K-AVS-SSG320
NS-DI-SSG350
NS-DI-SSG320
NS-WF-SSG350
NS-WF-SSG320
NS-SPAM2-SSG350
NS-SPAM2-SSG320
NS-RBO-CSSSG350
NS-RBO-CSSSG320
NS-SMB2-CSSSG350
NS-SMB2-CSSSG320
Antivirus (includes antispyware, antiphishing)
IPS (Deep Inspection)
Web filtering
Antispam
Remote Oce Bundle (includes AV, DI, WF)
Main Oce Bundle (includes AV, DI, WF, AS)
SSG300 Line Memory Upgrades, Spares
and Communications Cables
CBL-JX-PWR-AU Power cable, Australia
CBL-JX-PWR-CH Power cable, China
CBL-JX-PWR-EU Power cable, Europe
CBL-JX-PWR-IT Power cable, Italy
CBL-JX-PWR-JP Power cable, Japan
CBL-JX-PWR-UK Power cable, UK
CBL-JX-PWR-US Power cable, USA
SSG-300-MEM-1GB 1 Gigabyte memory upgrade for the SSG300 line
SSG-350-FLTR Replacement air filter for SSG300 line
JX-CBL-EIA530-DTE EIA530 cable (DTE)
JX-CBL-RS232-DTE RS232 cable (DTE)
JX-CBL-RS449-DTE RS449 cable (DTE)
JX-CBL-V35-DTE V.35 cable (DTE)
JX-CBL-X21-DT X.21 cable (DTE)
JX-Blank-FP-S Blank I/O plate
About Juniper Networks
Juniper Networks is in the business of network innovation. From
devices to data centers, from consumers to cloud providers,
Juniper Networks delivers the software, silicon and systems that
transform the experience and economics of networking. The
company serves customers and partners worldwide. Additional
information can be found at www.juniper.net.
Corporate and Sales Headquarters
Juniper Networks, Inc.
1194 North Mathilda Avenue
Sunny vale, CA 94089 USA
Phone: 888.JUNIPER (888.586.4737)
or 408.745.2000
Fax: 408.745.2100
www.juniper.net
Copyri ght 2013 Juniper Net works, Inc. All r ights reser ved. Junipe r Networks , the Juniper Net works logo, Jun os and
QFabric ar e registered tr ademarks of Ju niper Networ ks, Inc. in the Un ited States and othe r countries. Al l other
tradem arks, serv ice marks, re gistered mark s, or register ed service m arks are the pro perty of thei r respectiv e owners.
Junipe r Networks a ssumes no res ponsibilit y for any inaccurac ies in this docum ent. Juniper N etworks res erves the
right to ch ange, modify, tr ansfer, or other wise revise th is publicatio n without notice .
1000203-009-EN Sept 2013
8
Printed o n recycled pap er
APAC and EMEA Head quarters
Juniper Networks International B.V.
Boeing Avenue 240
1119 PZ Schiphol-Rijk
Amsterdam, The Netherlands
Phone: 31.0.207.125.700
Fax: 31.0.207.125.701
To purchase Juniper Networks solutions,
please contact your Juniper Networks
representative at 1-866-298-6428 or
authorized reseller.
 Loading...