

HP ProCurve MSM310-R, ProCurve MSM410, ProCurve MSM325, ProCurve MSM335, ProCurve MSM422 Reference Manual
...Page 1
ProCurve 5400zl Switches
Installation and Getting Started Guide
Reference Guide for HP ProCurve MSM3xx / MSM4xx Access Points CLI
HP ProCurve MSM3xx / MSM4xx Access Points CLI
Reference Guide
Page 2
Page 3
HP ProCurve
MSM3xx / MSM4xx Access Points
CLI Reference Guide
Page 4
Copyright and Disclaimer Notices
© Copyright 2010 Hewlett-Packard Development Company, L.P. The
information contained herein is subject to change without notice.
This document contains proprietary information, which is
protected by copyright. No part of this document may be
photocopied, reproduced, or translated into another language
without the prior written consent of Hewlett-Packard.
Publication Number
5998-0327
May 2010
Applicable Products
USA Japan WW
MSM310 Access Point J9374A/B J9524A/B J9379A/B
MSM310-R Access Point J9380A/B J9383A/B
MSM317 Access Device J9422A J9423A J9423A
MSM320 Access Point J9360A/B J9527A/B J9364A/B
MSM320-R Access Point J9365A/B J9528A/B J9368A/B
MSM325 Access Point
with Sensor
MSM335 Access Point
with Sensor
MSM410 Access Point J9426A/B J9529A/B J9427A/B
MSM422 Access Point J9358A/B J9530A/B J9359A/B
J9369A/B J9373A/B
J9356A/B J9357A/B
Disclaimer
HEWLETT-PACKARD COMPANY MAKES NO WARRANTY OF
ANY KIND WITH REGARD TO THIS MATERIAL, INCLUDING,
BUT NOT LIMITED TO, THE IMPLIED WARRANTIES OF
MERCHANTABILITY AND FITNESS FOR A PARTICULAR
PURPOSE. Hewlett-Packard shall not be liable for errors
contained herein or for incidental or consequential damages in
connection with the furnishing, performance, or use of this
material.
The only warranties for HP products and services are set forth
in the express warranty statements accompanying such
products and services. Nothing herein should be construed as
constituting an additional warranty. HP shall not be liable for
technical or editorial errors or omissions contained herein.
Hewlett-Packard assumes no responsibility for the use or
reliability of its software on equipment that is not furnished by
Hewlett-Packard.
Trademark Credits
Windows NT®, Windows®, and MS Windows® are US
registered trademarks of Microsoft Corporation.
Hewlett-Packard Company
8000 Foothills Boulevard
Roseville, California 95747
www.hp.com/go/procurve
Page 5
Contents
1 Introduction
About this guide ...........................................................................................................1-2
Products covered...................................................................................................1-2
Important terms..................................................................................................... 1-2
Typographical conventions ..................................................................................1-3
Command syntax ............................................................................................1-3
Management tool ............................................................................................1-3
New in this release.......................................................................................................1-3
HP ProCurve Networking support.............................................................................1-3
Before contacting support.............................................................................1-4
Online documentation .................................................................................................1-4
CLI support in autonomous and controlled modes .................................................1-4
Controlled mode....................................................................................................1-4
Autonomous mode ................................................................................................1-5
Configuring CLI support..............................................................................................1-5
Secure shell access.........................................................................................1-5
Authenticate CLI logins using .......................................................................1-5
Entering strings ............................................................................................................1-6
Context hierarchy ........................................................................................................1-7
Sample CLI session ......................................................................................................1-7
CLI commands
2
View context .................................................................................................................2-2
arping ......................................................................................................................2-2
enable......................................................................................................................2-2
iperf .........................................................................................................................2-2
nslookup ................................................................................................................. 2-2
ping..........................................................................................................................2-2
ps .............................................................................................................................2-3
quit...........................................................................................................................2-3
iii
Page 6

show license...........................................................................................................2-3
show logging filtered.............................................................................................2-3
top............................................................................................................................2-3
traceroute ...............................................................................................................2-3
Enable context..............................................................................................................2-4
reboot device..........................................................................................................2-4
show certificate .....................................................................................................2-4
show certificate binding ....................................................................................... 2-4
iperf .........................................................................................................................2-4
ping..........................................................................................................................2-4
arping ......................................................................................................................2-5
arp............................................................................................................................2-5
end...........................................................................................................................2-5
quit...........................................................................................................................2-5
rcapture...................................................................................................................2-5
show arp .................................................................................................................2-5
show bridge............................................................................................................2-6
show bridge forwarding........................................................................................2-6
show dns cache......................................................................................................2-6
show interfaces......................................................................................................2-6
show ip....................................................................................................................2-6
show ip route .........................................................................................................2-6
show system info ...................................................................................................2-6
New show wireless clients ............................................................................................2-6
New disassociate wireless client _...............................................................................2-7
factory reset ...........................................................................................................2-7
switch operational mode ......................................................................................2-7
show dot11 associations.......................................................................................2-7
show dot11 statistics client-traffic dot11n .........................................................2-7
show local mesh ....................................................................................................2-7
show wireless neighborhood ............................................................................... 2-7
show wireless rogue-ap ........................................................................................2-7
show client log.......................................................................................................2-8
show discrete pin...................................................................................................2-8
config.......................................................................................................................2-8
show all config.......................................................................................................2-8
Config context ..............................................................................................................2-9
certificate................................................................................................................2-9
iv
Page 7
certificate binding..................................................................................................2-9
certificate revocation ............................................................................................2-9
end...........................................................................................................................2-9
factory settings ......................................................................................................2-9
interface ethernet ..................................................................................................2-9
New network-profile ....................................................................................................2-10
reboot device........................................................................................................2-10
show certificate ...................................................................................................2-10
show certificate binding ..................................................................................... 2-10
show config factory.............................................................................................2-10
New show network-profiles........................................................................................2-10
interface ip............................................................................................................2-10
interface wireless ................................................................................................2-11
local mesh profile ................................................................................................2-11
interface gre .........................................................................................................2-11
virtual ap...............................................................................................................2-11
cap-switch to........................................................................................................2-11
admin local authentication.................................................................................2-12
admin radius authentication ..............................................................................2-12
admin radius authentication server ..................................................................2-12
ip http port............................................................................................................2-12
ip https port..........................................................................................................2-12
snmp-server trap certificate-expired.................................................................2-12
snmp-server trap certificate-expires-soon .......................................................2-13
snmp-server trap web-fail...................................................................................2-13
snmp-server trap web-login................................................................................2-13
snmp-server trap web-logout .............................................................................2-13
username ..............................................................................................................2-13
web admin kickout..............................................................................................2-14
web allow..............................................................................................................2-14
world-mode dot11 country code........................................................................2-14
web access port-1 ................................................................................................2-14
web access port-2 ................................................................................................2-14
web access wireless ............................................................................................2-15
web access interface vlan...................................................................................2-15
web access interface gre ....................................................................................2-15
web access local mesh........................................................................................2-15
New console authentication........................................................................................2-15
clock......................................................................................................................2-16
v
Page 8
clock auto adjust dst ...........................................................................................2-16
clock timezone.....................................................................................................2-16
clock use custom dst rules.................................................................................2-16
ntp protocol..........................................................................................................2-16
ntp server..............................................................................................................2-17
clock custom dst begins .....................................................................................2-17
clock custom dst begins format.........................................................................2-17
clock custom dst ends ........................................................................................2-17
clock custom dst ends format............................................................................2-18
ntp server..............................................................................................................2-18
ntp server failure trap .........................................................................................2-18
config-update automatic.....................................................................................2-18
config-update operation......................................................................................2-19
New config-update start ..............................................................................................2-19
config-update time...............................................................................................2-19
config-update uri..................................................................................................2-19
config-update weekday.......................................................................................2-19
snmp-server trap config-change ........................................................................2-19
snmp-server trap config-update.........................................................................2-20
logging destination ..............................................................................................2-20
snmp-server trap syslog-severity .......................................................................2-20
snmp-server..........................................................................................................2-20
snmp-server access port-1..................................................................................2-20
snmp-server allow ...............................................................................................2-21
snmp-server chassis-id........................................................................................2-21
snmp-server contact............................................................................................2-21
snmp-server heartbeat period............................................................................2-21
snmp-server location...........................................................................................2-21
snmp-server port..................................................................................................2-22
snmp-server readonly..........................................................................................2-22
snmp-server readwrite........................................................................................2-22
snmp-server trap..................................................................................................2-22
snmp-server trap community.............................................................................2-22
snmp-server trap destination ............................................................................. 2-23
snmp-server trap heartbeat ................................................................................2-23
snmp-server trap link-state.................................................................................2-23
snmp-server trap snmp-authentication.............................................................2-23
snmp-server version 1.........................................................................................2-23
snmp-server version 2c.......................................................................................2-24
vi
Page 9
snmp-server version 3.........................................................................................2-24
snmp-server access interface vlan ....................................................................2-24
snmp-server access local mesh..........................................................................2-24
snmp-server access interface gre ......................................................................2-24
snmp-server access wireless..............................................................................2-25
snmp-server access port-2..................................................................................2-25
snmp-server user .................................................................................................2-25
snmp-server notification receiver .....................................................................2-25
soap-server ...........................................................................................................2-25
soap-server access interface vlan......................................................................2-26
soap-server access port-1 ...................................................................................2-26
soap-server access port-2 ...................................................................................2-26
soap-server allow.................................................................................................2-26
soap-server http authentication.........................................................................2-26
soap-server http authentication password.......................................................2-27
soap-server http authentication username.......................................................2-27
soap-server port...................................................................................................2-27
soap-server ssl......................................................................................................2-27
soap-server ssl with client certificate ...............................................................2-27
soap-server access interface gre........................................................................2-27
soap-server access wireless ...............................................................................2-28
soap-server access local mesh...........................................................................2-28
snmp-server trap low-snr....................................................................................2-28
snmp-server trap low-snr interval .....................................................................2-28
snmp-server trap low-snr level ..........................................................................2-28
snmp-server trap new-association.....................................................................2-28
snmp-server trap new-association interval ......................................................2-29
snmp-server trap vpn-connection......................................................................2-29
snmp-server trap wireless-association-fail.......................................................2-29
snmp-server trap wireless-association-success...............................................2-29
snmp-server trap wireless-authentication-fail .................................................2-29
snmp-server trap wireless-authentication-success .........................................2-29
snmp-server trap wireless-deauthentication-fail .............................................2-30
snmp-server trap wireless-deauthentication-success .....................................2-30
snmp-server trap wireless-disassociation-fail.................................................. 2-30
snmp-server trap wireless-disassociation-success.......................................... 2-30
snmp-server trap wireless-reassociation-fail ...................................................2-30
snmp-server trap wireless-reassociation-success ...........................................2-30
snmp-server trap syslog-matches ......................................................................2-31
vii
Page 10
snmp-server trap syslog-matches regex ...........................................................2-31
snmp-server trap syslog-severity level..............................................................2-31
snmp-server trap network-trace ........................................................................2-31
firmware-update automatic................................................................................2-31
firmware-update start .........................................................................................2-32
firmware-update time..........................................................................................2-32
firmware-update uri ............................................................................................2-32
firmware-update weekday..................................................................................2-32
snmp-server trap firmware-update....................................................................2-32
access-controller restrict location.....................................................................2-33
service-sensor ......................................................................................................2-33
service-sensor ......................................................................................................2-33
service-sensor poll...............................................................................................2-33
service-sensor retry.............................................................................................2-34
service-sensor timeout........................................................................................2-34
ip name-server......................................................................................................2-34
ip name-server cache ..........................................................................................2-34
ip name-server dynamic......................................................................................2-35
New ip name-server interception ............................................................................... 2-35
ip name-server switch-on-servfail .....................................................................2-35
ip name-server switch-over ................................................................................2-35
snmp-server trap unauthorized-ap ....................................................................2-35
snmp-server trap unauthorized-ap interval ......................................................2-36
wireless-scan........................................................................................................2-36
wireless-scan period............................................................................................2-36
wireless-scan url ..................................................................................................2-36
access controller shared secret .........................................................................2-36
radius-server profile ............................................................................................2-37
ip-qos profile ........................................................................................................2-37
dot11 igmp snooping-helper...............................................................................2-37
New lldp config.............................................................................................................2-37
New lldp dynamic-name ..............................................................................................2-37
New lldp dynamic-name refresh-time........................................................................2-38
New lldp dynamic-name user-string...........................................................................2-38
New lldp fast-start-count .............................................................................................2-38
New lldp holdtime-multiplier......................................................................................2-38
New lldp med-location civic-address-element..........................................................2-38
New lldp med-location elin-addr ................................................................................2-39
New lldp refresh-interval.............................................................................................2-39
viii
Page 11
New lldp run..................................................................................................................2-39
New show lldp config...................................................................................................2-39
New show lldp info local-device.................................................................................2-39
New show lldp info remote-device.............................................................................2-39
New show lldp stats .....................................................................................................2-39
New lldp local-mesh.....................................................................................................2-40
discovery protocol...............................................................................................2-40
discovery protocol device-id..............................................................................2-40
New service controller discovery interface internet-port.......................................2-40
New service controller discovery interface lan-port ...............................................2-40
bridge priority ......................................................................................................2-41
bridge protocol ieee ............................................................................................2-41
bridge protocol ieee vlan....................................................................................2-41
ip route gateway ..................................................................................................2-41
dot1x reauth .........................................................................................................2-42
dot1x reauth period.............................................................................................2-42
dot1x reauth terminate ....................................................................................... 2-42
dot1x supplicant timeout....................................................................................2-42
dynamic key .........................................................................................................2-42
dynamic key interval ...........................................................................................2-43
add wireless ip-qos profile..................................................................................2-43
delete wireless ip-qos profile all ........................................................................2-43
delete wireless ip-qos profile .............................................................................2-43
wireless link qos ..................................................................................................2-43
sensor discovery mode .......................................................................................2-43
sensor network detector.....................................................................................2-44
sensor server id....................................................................................................2-44
sensor server name .............................................................................................2-44
config-version.......................................................................................................2-44
New sflow......................................................................................................................2-45
New show sflow agent .................................................................................................2-45
New show sflow controller stats ................................................................................2-45
New show sflow device stats ......................................................................................2-45
New sflow destination .................................................................................................2-45
New show sflow destination.......................................................................................2-45
New show sflow sampling-polling..............................................................................2-45
New sflow sampling .....................................................................................................2-46
New sflow polling.........................................................................................................2-46
New mac lockout entry................................................................................................2-46
ix
Page 12
New show mac lockout ...............................................................................................2-46
New supplicant 802dot1x ............................................................................................2-46
New supplicant anonymous identity..........................................................................2-46
New supplicant eap......................................................................................................2-46
Port 2 port interface context ....................................................................................2-47
end.........................................................................................................................2-47
duplex ...................................................................................................................2-47
speed ..................................................................................................................... 2-47
vlan ........................................................................................................................2-47
vlan compatibility mode ..................................................................................... 2-48
vlan-management filter .......................................................................................2-48
interface vlan........................................................................................................2-48
Port 1 port interface context ....................................................................................2-49
end.........................................................................................................................2-49
duplex ...................................................................................................................2-49
speed ..................................................................................................................... 2-49
vlan ........................................................................................................................2-49
vlan compatibility mode ..................................................................................... 2-50
vlan-management filter .......................................................................................2-50
interface vlan........................................................................................................2-50
WAN IP interface context..........................................................................................2-51
pppoe client user .................................................................................................2-51
ip address mode...................................................................................................2-51
ip address..............................................................................................................2-51
ip default-gateway ...............................................................................................2-51
ip address dhcp client-id.....................................................................................2-52
end.........................................................................................................................2-52
pppoe auto-reconnect .........................................................................................2-52
pppoe mru ............................................................................................................2-52
pppoe mtu.............................................................................................................2-52
pppoe unnumbered .............................................................................................2-53
Wireless context.........................................................................................................2-54
end.........................................................................................................................2-54
radio active...........................................................................................................2-54
rts threshold .........................................................................................................2-54
distance.................................................................................................................2-54
dot11......................................................................................................................2-55
x
Page 13

transmit power..................................................................................................... 2-55
antenna bidirectionnal........................................................................................2-56
antenna gain .........................................................................................................2-56
autochannel skip..................................................................................................2-56
beacon interval ....................................................................................................2-56
dot11 automatic frequency.................................................................................2-56
dot11 automatic frequency period ....................................................................2-57
dot11 automatic frequency time........................................................................2-57
dot11 automatic transmit-power .......................................................................2-57
dot11 automatic transmit-power period...........................................................2-57
New maximum clients .................................................................................................2-57
multicast rate .......................................................................................................2-57
station distance....................................................................................................2-58
dot11 mode...........................................................................................................2-58
spectralink view...................................................................................................2-58
New dot11n channel extension...................................................................................2-58
dot11n channel width..........................................................................................2-58
New dot11n guard interval ..........................................................................................2-58
dot11n mimo ........................................................................................................2-59
New dot11n multicast rate ..........................................................................................2-59
bandwidth.............................................................................................................2-59
bandwidth max .................................................................................................... 2-59
Virtual AP context......................................................................................................2-60
virtual ap name ....................................................................................................2-60
ingress interface ..................................................................................................2-60
guest-mode ...........................................................................................................2-60
max-association ...................................................................................................2-60
ssid name..............................................................................................................2-60
vlan ........................................................................................................................2-61
encryption key 1 ..................................................................................................2-61
encryption key format.........................................................................................2-61
transmit key..........................................................................................................2-61
authentication server access controller ...........................................................2-62
authentication server accounting......................................................................2-62
authentication server accounting radius profile .............................................2-62
authentication server radius ..............................................................................2-62
dot1x authentication ...........................................................................................2-62
wpa-psk.................................................................................................................2-62
authentication server accounting radius stationid case.................................2-63
xi
Page 14
authentication server accounting radius stationid delimiter.........................2-63
wireless filters......................................................................................................2-63
wireless filters mac .............................................................................................2-63
wireless filters rule input....................................................................................2-63
wireless filters rule output .................................................................................2-64
wireless filters type .............................................................................................2-64
mac-filters local ...................................................................................................2-65
mac-filters.............................................................................................................2-65
mac-filters mode ..................................................................................................2-66
mac authentication accounting .........................................................................2-66
mac authentication accounting radius profile.................................................2-66
mac authentication radius profile .....................................................................2-66
mac authentication radius stationid case.........................................................2-66
mac authentication radius stationid delimiter.................................................2-67
mac authentication..............................................................................................2-67
add ip filter ...........................................................................................................2-67
delete ip filter .......................................................................................................2-67
delete ip filter all..................................................................................................2-67
ip filters.................................................................................................................2-68
active.....................................................................................................................2-68
beacon dtim count...............................................................................................2-68
beacon transmit power.......................................................................................2-68
New data rate................................................................................................................2-68
add ip-qos profile.................................................................................................2-69
delete ip-qos profile all........................................................................................2-69
delete ip-qos profile.............................................................................................2-69
qos .........................................................................................................................2-69
upstream diffserv tagging...................................................................................2-70
wmm advertising .................................................................................................2-70
location-aware group ..........................................................................................2-70
end.........................................................................................................................2-71
security .................................................................................................................2-71
VLAN interface context .............................................................................................2-72
end.........................................................................................................................2-72
ip address..............................................................................................................2-72
ip address mode...................................................................................................2-72
Local mesh context....................................................................................................2-73
end.........................................................................................................................2-73
xii
Page 15
active.....................................................................................................................2-73
interface................................................................................................................2-73
local mesh name ..................................................................................................2-73
remote mac...........................................................................................................2-73
security .................................................................................................................2-74
security mode....................................................................................................... 2-74
security psk ..........................................................................................................2-74
security wep .........................................................................................................2-74
speed ..................................................................................................................... 2-74
interface vlan........................................................................................................2-74
accept forced links ..............................................................................................2-75
allowed downtime ...............................................................................................2-75
dynamic local mesh.............................................................................................2-75
dynamic mode......................................................................................................2-75
initial discovery time...........................................................................................2-75
mesh id..................................................................................................................2-76
minimum snr ........................................................................................................2-76
preserve master link............................................................................................2-76
promiscuous mode..............................................................................................2-76
promiscuous mode startup delay ......................................................................2-77
snr cost per hop ...................................................................................................2-77
RADIUS profiles context...........................................................................................2-78
end.........................................................................................................................2-78
radius-server accounting port............................................................................2-78
radius-server alternate hosts..............................................................................2-78
radius-server authentication method................................................................ 2-78
radius-server authentication port......................................................................2-78
radius-server deadtime .......................................................................................2-79
radius-server host ................................................................................................2-79
radius-server key 2 ..............................................................................................2-79
radius-server message-authenticator................................................................2-79
radius-server name ..............................................................................................2-79
radius-server nasid ..............................................................................................2-80
radius-server timeout ..........................................................................................2-80
radius-server timeout ..........................................................................................2-80
IP QOS context ...........................................................................................................2-81
end.........................................................................................................................2-81
end-port.................................................................................................................2-81
xiii
Page 16
priority ..................................................................................................................2-81
profile name .........................................................................................................2-81
protocol.................................................................................................................2-81
start-port ...............................................................................................................2-81
GRE interface context ...............................................................................................2-83
end force...............................................................................................................2-83
gre name ...............................................................................................................2-83
ip address..............................................................................................................2-83
peer ip address.....................................................................................................2-83
remote ip address ................................................................................................2-83
Syslog context ............................................................................................................2-84
active.....................................................................................................................2-84
logging facility......................................................................................................2-84
logging host ..........................................................................................................2-84
logging prefix .......................................................................................................2-84
name......................................................................................................................2-84
end.........................................................................................................................2-85
level .......................................................................................................................2-85
level .......................................................................................................................2-85
matches.................................................................................................................2-85
message.................................................................................................................2-85
message.................................................................................................................2-86
process..................................................................................................................2-86
process..................................................................................................................2-86
SNMP user context ....................................................................................................2-87
access level...........................................................................................................2-87
end.........................................................................................................................2-87
password...............................................................................................................2-87
security .................................................................................................................2-87
user name .............................................................................................................2-87
SNMP notification receiver context ........................................................................2-88
community............................................................................................................2-88
end.........................................................................................................................2-88
port ........................................................................................................................2-88
receiver .................................................................................................................2-88
user........................................................................................................................2-88
version...................................................................................................................2-88
xiv
Page 17
Network profile context............................................................................................2-89
New end.........................................................................................................................2-89
New name......................................................................................................................2-89
New vlan ........................................................................................................................2-89
New vlan ........................................................................................................................2-89
LLDP agent context ...................................................................................................2-90
New admin-status .........................................................................................................2-90
New basic-tlv-enable ....................................................................................................2-90
New basic-tlv-enable port_desc..................................................................................2-90
New basic-tlv-enable system_cap...............................................................................2-90
New basic-tlv-enable system_descr ...........................................................................2-90
New basic-tlv-enable system_name ...........................................................................2-91
New dot3-tlv-enable .....................................................................................................2-91
New end.........................................................................................................................2-91
New ip-addr-enable.......................................................................................................2-91
New med-application-type...........................................................................................2-91
New medtlv-enable capabilities..................................................................................2-91
New medtlv-enable location-id ...................................................................................2-92
New medtlv-enable network-policy ...........................................................................2-92
New medtlv-enable poe ...............................................................................................2-92
xv
Page 18
xvi
Page 19
Alphabetical list of commands
accept forced links ...................................................... 2-75
access controller shared secret ................................. 2-36
access level................................................................... 2-87
access-controller restrict location............................. 2-33
active ............................................................................. 2-68
active ............................................................................. 2-73
active ............................................................................. 2-84
add ip filter ................................................................... 2-67
add ip-qos profile ......................................................... 2-69
add wireless ip-qos profile.......................................... 2-43
admin local authentication......................................... 2-12
admin radius authentication server .......................... 2-12
admin radius authentication ...................................... 2-12
New admin-status ................................................................. 2-90
allowed downtime ....................................................... 2-75
antenna bidirectionnal ................................................ 2-56
antenna gain ................................................................. 2-56
arp.................................................................................... 2-5
arping .............................................................................. 2-2
arping .............................................................................. 2-5
authentication server access controller ................... 2-62
authentication server accounting radius profile ..... 2-62
authentication server accounting radius stationid case2-63
authentication server accounting radius stationid delimiter
2-63
authentication server accounting.............................. 2-62
authentication server radius ...................................... 2-62
autochannel skip.......................................................... 2-56
bandwidth max ............................................................ 2-59
bandwidth..................................................................... 2-59
New basic-tlv-enable port_desc .......................................... 2-90
New basic-tlv-enable system_cap....................................... 2-90
New basic-tlv-enable system_descr ................................... 2-90
New basic-tlv-enable system_name ................................... 2-91
New basic-tlv-enable ............................................................ 2-90
beacon dtim count....................................................... 2-68
beacon interval ............................................................ 2-56
beacon transmit power ............................................... 2-68
bridge priority .............................................................. 2-41
bridge protocol ieee vlan ............................................ 2-41
bridge protocol ieee .................................................... 2-41
cap-switch to ................................................................ 2-11
certificate binding.......................................................... 2-9
certificate revocation .................................................... 2-9
certificate........................................................................ 2-9
clock auto adjust dst ................................................... 2-16
clock custom dst begins format................................. 2-17
clock custom dst begins ............................................. 2-17
clock custom dst ends format.................................... 2-18
clock custom dst ends ................................................ 2-17
clock timezone............................................................. 2-16
clock use custom dst rules ......................................... 2-16
clock.............................................................................. 2-16
community.................................................................... 2-88
config............................................................................... 2-8
config-update automatic ............................................. 2-18
config-update operation.............................................. 2-19
New config-update start ...................................................... 2-19
config-update time....................................................... 2-19
config-update uri.......................................................... 2-19
config-update weekday ............................................... 2-19
config-version............................................................... 2-44
New console authentication................................................ 2-15
New data rate .........................................................................2-68
delete ip filter all...........................................................2-67
delete ip filter ................................................................2-67
delete ip-qos profile all.................................................2-69
delete ip-qos profile......................................................2-69
delete wireless ip-qos profile all .................................2-43
delete wireless ip-qos profile ......................................2-43
New disassociate wireless client _ ........................................2-7
discovery protocol device-id .......................................2-40
discovery protocol........................................................2-40
distance..........................................................................2-54
dot11 automatic frequency period .............................2-57
dot11 automatic frequency time .................................2-57
dot11 automatic frequency..........................................2-56
dot11 automatic transmit-power period ....................2-57
dot11 automatic transmit-power ................................2-57
dot11 igmp snooping-helper........................................2-37
dot11 mode....................................................................2-58
dot11...............................................................................2-55
New dot11n channel extension ...........................................2-58
dot11n channel width...................................................2-58
New dot11n guard interval ...................................................2-58
dot11n mimo .................................................................2-59
New dot11n multicast rate ...................................................2-59
dot1x authentication ....................................................2-62
dot1x reauth period......................................................2-42
dot1x reauth terminate ................................................2-42
dot1x reauth ..................................................................2-42
dot1x supplicant timeout.............................................2-42
New dot3-tlv-enable ..............................................................2-91
duplex ............................................................................2-47
duplex ............................................................................2-49
dynamic key interval ....................................................2-43
dynamic key ..................................................................2-42
dynamic local mesh......................................................2-75
dynamic mode...............................................................2-75
enable...............................................................................2-2
encryption key 1 ...........................................................2-61
encryption key format..................................................2-61
end force........................................................................2-83
end..................................................................................2-47
end-port..........................................................................2-81
factory reset ....................................................................2-7
factory settings ...............................................................2-9
firmware-update automatic.........................................2-31
firmware-update start ..................................................2-32
firmware-update time...................................................2-32
firmware-update uri .....................................................2-32
firmware-update weekday...........................................2-32
gre name ........................................................................2-83
guest-mode ....................................................................2-60
ingress interface ...........................................................2-60
initial discovery time....................................................2-75
interface ethernet ...........................................................2-9
interface gre ..................................................................2-11
interface ip.....................................................................2-10
interface vlan.................................................................2-48
interface vlan.................................................................2-50
interface vlan.................................................................2-74
interface wireless .........................................................2-11
interface.........................................................................2-73
ip address dhcp client-id..............................................2-52
ip address mode............................................................2-51
xvii
Page 20
ip address mode........................................................... 2-72
ip address...................................................................... 2-51
ip address...................................................................... 2-72
ip address...................................................................... 2-83
ip default-gateway ....................................................... 2-51
ip filters......................................................................... 2-68
ip http port.................................................................... 2-12
ip https port.................................................................. 2-12
ip name-server cache .................................................. 2-34
ip name-server dynamic.............................................. 2-35
New ip name-server interception ....................................... 2-35
ip name-server switch-on-servfail ............................. 2-35
ip name-server switch-over ........................................ 2-35
ip name-server.............................................................. 2-34
ip route gateway .......................................................... 2-41
New ip-addr-enable............................................................... 2-91
iperf ................................................................................. 2-2
iperf ................................................................................. 2-4
ip-qos profile ................................................................ 2-37
level ............................................................................... 2-85
level ............................................................................... 2-85
New lldp config..................................................................... 2-37
New lldp dynamic-name refresh-time ................................ 2-38
New lldp dynamic-name user-string................................... 2-38
New lldp dynamic-name ...................................................... 2-37
New lldp fast-start-count ..................................................... 2-38
New lldp holdtime-multiplier .............................................. 2-38
New lldp local-mesh ............................................................. 2-40
New lldp med-location civic-address-element .................. 2-38
New lldp med-location elin-addr ........................................ 2-39
New lldp refresh-interval ..................................................... 2-39
New lldp run.......................................................................... 2-39
local mesh name .......................................................... 2-73
local mesh profile ........................................................ 2-11
location-aware group .................................................. 2-70
logging destination ...................................................... 2-20
logging facility.............................................................. 2-84
logging host .................................................................. 2-84
logging prefix ............................................................... 2-84
mac authentication accounting radius profile ......... 2-66
mac authentication accounting ................................. 2-66
mac authentication radius profile ............................. 2-66
mac authentication radius stationid case ................. 2-66
mac authentication radius stationid delimiter ......... 2-67
mac authentication...................................................... 2-67
New mac lockout entry........................................................ 2-46
mac-filters local ........................................................... 2-65
mac-filters mode .......................................................... 2-66
mac-filters..................................................................... 2-65
matches......................................................................... 2-85
max-association ........................................................... 2-60
New maximum clients ......................................................... 2-57
New med-application-type................................................... 2-91
New medtlv-enable capabilities.......................................... 2-91
New medtlv-enable location-id ........................................... 2-92
New medtlv-enable network-policy ................................... 2-92
New medtlv-enable poe ....................................................... 2-92
mesh id.......................................................................... 2-76
message......................................................................... 2-85
message......................................................................... 2-86
minimum snr ................................................................ 2-76
multicast rate ............................................................... 2-57
name.............................................................................. 2-84
New name.............................................................................. 2-89
New network-profile ............................................................ 2-10
nslookup ......................................................................... 2-2
ntp protocol .................................................................. 2-16
ntp server failure trap.................................................. 2-18
ntp server ...................................................................... 2-17
ntp server ...................................................................... 2-18
password ....................................................................... 2-87
peer ip address ............................................................. 2-83
ping .................................................................................. 2-2
ping .................................................................................. 2-4
port................................................................................. 2-88
pppoe auto-reconnect.................................................. 2-52
pppoe client user.......................................................... 2-51
pppoe mru..................................................................... 2-52
pppoe mtu ..................................................................... 2-52
pppoe unnumbered...................................................... 2-53
preserve master link .................................................... 2-76
priority........................................................................... 2-81
process .......................................................................... 2-86
process .......................................................................... 2-86
profile name.................................................................. 2-81
promiscuous mode startup delay............................... 2-77
promiscuous mode ...................................................... 2-76
protocol ......................................................................... 2-81
ps...................................................................................... 2-3
qos.................................................................................. 2-69
quit ................................................................................... 2-3
quit ................................................................................... 2-5
radio active ................................................................... 2-54
radius-server accounting port .................................... 2-78
radius-server alternate hosts ...................................... 2-78
radius-server authentication method ........................ 2-78
radius-server authentication port .............................. 2-78
radius-server deadtime................................................ 2-79
radius-server host ........................................................ 2-79
radius-server key 2....................................................... 2-79
radius-server message-authenticator ........................ 2-79
radius-server name ...................................................... 2-79
radius-server nasid....................................................... 2-80
radius-server profile .................................................... 2-37
radius-server timeout .................................................. 2-80
radius-server timeout .................................................. 2-80
rcapture ........................................................................... 2-5
reboot device ................................................................ 2-10
reboot device .................................................................. 2-4
receiver.......................................................................... 2-88
remote ip address......................................................... 2-83
remote mac ................................................................... 2-73
rts threshold.................................................................. 2-54
security mode ............................................................... 2-74
security psk................................................................... 2-74
security wep.................................................................. 2-74
security.......................................................................... 2-71
security.......................................................................... 2-74
security.......................................................................... 2-87
sensor discovery mode................................................ 2-43
sensor network detector ............................................. 2-44
sensor server id ............................................................ 2-44
sensor server name...................................................... 2-44
New service controller discovery interface internet-port 2-40
New service controller discovery interface lan-port........ 2-40
service-sensor poll ....................................................... 2-33
service-sensor retry ..................................................... 2-34
service-sensor timeout ................................................ 2-34
service-sensor............................................................... 2-33
service-sensor............................................................... 2-33
New sflow destination.......................................................... 2-45
New sflow polling ................................................................. 2-46
xviii
Page 21
New sflow sampling ............................................................. 2-46
New sflow.............................................................................. 2-45
show all config ............................................................... 2-8
show arp ......................................................................... 2-5
show bridge forwarding................................................ 2-6
show bridge .................................................................... 2-6
show certificate binding ............................................. 2-10
show certificate binding ............................................... 2-4
show certificate ........................................................... 2-10
show certificate ............................................................. 2-4
show client log ............................................................... 2-8
show config factory..................................................... 2-10
show discrete pin........................................................... 2-8
show dns cache.............................................................. 2-6
show dot11 associations............................................... 2-7
show dot11 statistics client-traffic dot11n ................. 2-7
show interfaces.............................................................. 2-6
show ip route ................................................................. 2-6
show ip............................................................................ 2-6
show license................................................................... 2-3
New show lldp config........................................................... 2-39
New show lldp info local-device......................................... 2-39
New show lldp info remote-device..................................... 2-39
New show lldp stats ............................................................. 2-39
show local mesh ............................................................ 2-7
show logging filtered..................................................... 2-3
New show mac lockout ....................................................... 2-46
New show network-profiles ................................................ 2-10
New show sflow agent ......................................................... 2-45
New show sflow controller stats ........................................ 2-45
New show sflow destination ............................................... 2-45
New show sflow device stats .............................................. 2-45
New show sflow sampling-polling...................................... 2-45
show system info ........................................................... 2-6
New show wireless clients .................................................... 2-6
show wireless neighborhood ....................................... 2-7
show wireless rogue-ap ................................................ 2-7
snmp-server access interface gre .............................. 2-24
snmp-server access interface vlan ............................ 2-24
snmp-server access local mesh.................................. 2-24
snmp-server access port-1 .......................................... 2-20
snmp-server access port-2 .......................................... 2-25
snmp-server access wireless ...................................... 2-25
snmp-server allow ....................................................... 2-21
snmp-server chassis-id................................................ 2-21
snmp-server contact.................................................... 2-21
snmp-server heartbeat period .................................... 2-21
snmp-server location................................................... 2-21
snmp-server notification receiver ............................. 2-25
snmp-server port.......................................................... 2-22
snmp-server readonly.................................................. 2-22
snmp-server readwrite ................................................ 2-22
snmp-server trap certificate-expired......................... 2-12
snmp-server trap certificate-expires-soon ............... 2-13
snmp-server trap community ..................................... 2-22
snmp-server trap config-change ................................ 2-19
snmp-server trap config-update................................. 2-20
snmp-server trap destination ..................................... 2-23
snmp-server trap firmware-update............................ 2-32
snmp-server trap heartbeat ........................................ 2-23
snmp-server trap link-state......................................... 2-23
snmp-server trap low-snr interval ............................. 2-28
snmp-server trap low-snr level .................................. 2-28
snmp-server trap low-snr............................................ 2-28
snmp-server trap network-trace ................................ 2-31
snmp-server trap new-association interval .............. 2-29
snmp-server trap new-association .............................2-28
snmp-server trap snmp-authentication ..................... 2-23
snmp-server trap syslog-matches regex .................... 2-31
snmp-server trap syslog-matches............................... 2-31
snmp-server trap syslog-severity level ...................... 2-31
snmp-server trap syslog-severity ............................... 2-20
snmp-server trap unauthorized-ap interval .............. 2-36
snmp-server trap unauthorized-ap............................. 2-35
snmp-server trap vpn-connection .............................. 2-29
snmp-server trap web-fail ........................................... 2-13
snmp-server trap web-login ........................................ 2-13
snmp-server trap web-logout...................................... 2-13
snmp-server trap wireless-association-fail ............... 2-29
snmp-server trap wireless-association-success .......2-29
snmp-server trap wireless-authentication-fail..........2-29
snmp-server trap wireless-authentication-success..2-29
snmp-server trap wireless-deauthentication-fail .....2-30
snmp-server trap wireless-deauthentication-success2-30
snmp-server trap wireless-disassociation-fail ..........2-30
snmp-server trap wireless-disassociation-success ..2-30
snmp-server trap wireless-reassociation-fail............ 2-30
snmp-server trap wireless-reassociation-success....2-30
snmp-server trap .......................................................... 2-22
snmp-server user.......................................................... 2-25
snmp-server version 1 ................................................. 2-23
snmp-server version 2c ............................................... 2-24
snmp-server version 3 ................................................. 2-24
snmp-server .................................................................. 2-20
snr cost per hop............................................................ 2-77
soap-server access interface gre ................................ 2-27
soap-server access interface vlan .............................. 2-26
soap-server access local mesh ................................... 2-28
soap-server access port-1............................................ 2-26
soap-server access port-2............................................ 2-26
soap-server access wireless........................................ 2-28
soap-server allow ......................................................... 2-26
soap-server http authentication password ............... 2-27
soap-server http authentication username ............... 2-27
soap-server http authentication ................................. 2-26
soap-server port ........................................................... 2-27
soap-server ssl with client certificate........................2-27
soap-server ssl .............................................................. 2-27
soap-server.................................................................... 2-25
spectralink view ........................................................... 2-58
speed.............................................................................. 2-47
speed.............................................................................. 2-49
speed.............................................................................. 2-74
ssid name ...................................................................... 2-60
start-port ....................................................................... 2-81
station distance ............................................................ 2-58
New supplicant 802dot1x..................................................... 2-46
New supplicant anonymous identity .................................. 2-46
New supplicant eap .............................................................. 2-46
switch operational mode............................................... 2-7
top .................................................................................... 2-3
traceroute........................................................................ 2-3
transmit key .................................................................. 2-61
transmit power ............................................................. 2-55
upstream diffserv tagging ........................................... 2-70
user name...................................................................... 2-87
user ................................................................................ 2-88
username....................................................................... 2-13
version ........................................................................... 2-88
virtual ap name............................................................. 2-60
virtual ap ....................................................................... 2-11
vlan compatibility mode.............................................. 2-48
xix
Page 22
vlan compatibility mode ............................................. 2-50
vlan ................................................................................ 2-47
vlan-management filter ............................................... 2-48
vlan-management filter ............................................... 2-50
web access interface gre ............................................ 2-15
web access interface vlan........................................... 2-15
web access local mesh................................................ 2-15
web access port-1 ........................................................ 2-14
web access port-2 ........................................................ 2-14
web access wireless .................................................... 2-15
web admin kickout...................................................... 2-14
web allow...................................................................... 2-14
wireless filters mac ..................................................... 2-63
wireless filters rule input............................................ 2-63
wireless filters rule output ......................................... 2-64
wireless filters type ..................................................... 2-64
wireless filters.............................................................. 2-63
wireless link qos .......................................................... 2-43
wireless-scan period.................................................... 2-36
wireless-scan url .......................................................... 2-36
wireless-scan ................................................................ 2-36
wmm advertising ......................................................... 2-70
world-mode dot11 country code................................ 2-14
wpa-psk......................................................................... 2-62
xx
Page 23
Chapter 1: Introduction
Introduction
Contents
About this guide ...........................................................................................................1-2
Products covered...................................................................................................1-2
Important terms..................................................................................................... 1-2
Typographical conventions ..................................................................................1-3
New in this release.......................................................................................................1-3
HP ProCurve Networking support.............................................................................1-3
1
Online documentation .................................................................................................1-4
CLI support in autonomous and controlled modes .................................................1-4
Controlled mode....................................................................................................1-4
Autonomous mode ................................................................................................1-5
Configuring CLI support..............................................................................................1-5
Entering strings ............................................................................................................1-6
Context hierarchy ........................................................................................................1-7
Sample CLI session ......................................................................................................1-7
Online documentation .................................................................................................1-4
Page 24
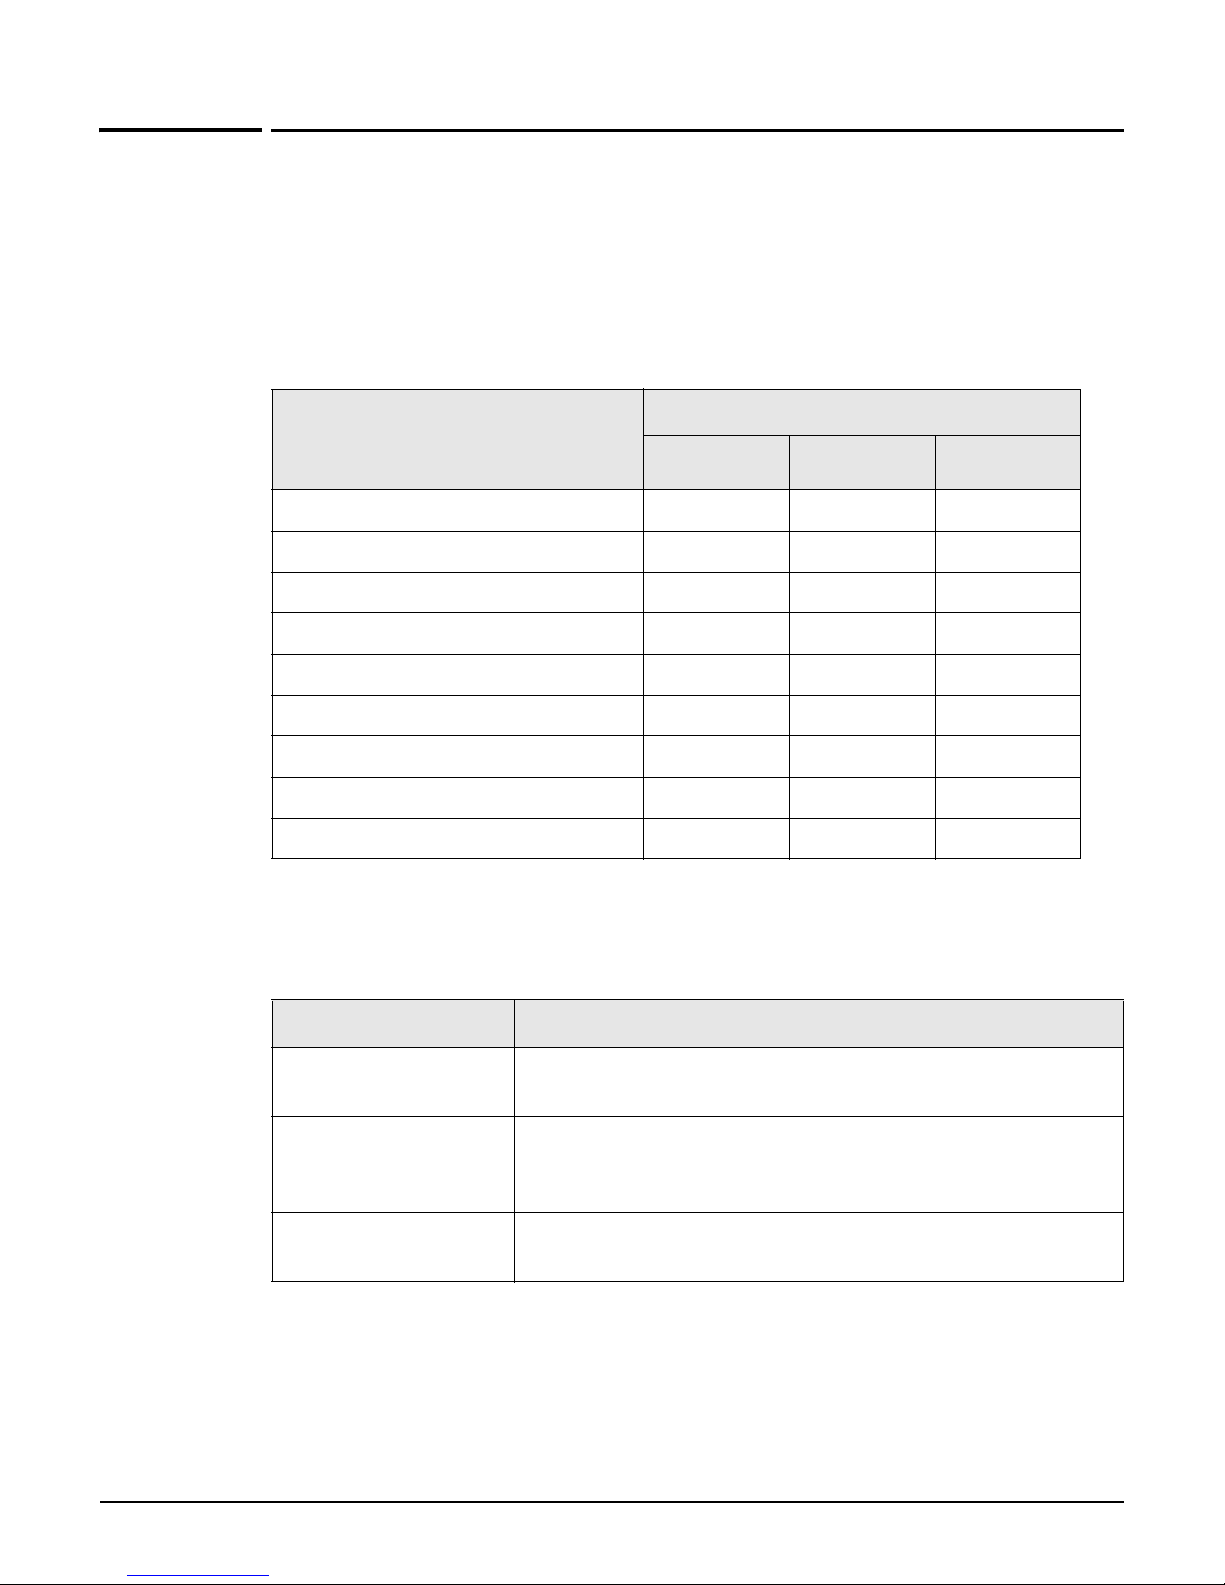
Introduction
About this guide
About this guide
This guide explains how to work with the Command Line Interface (CLI) on HP ProCurve
Networking MSM3xx and MSM4xx APs.
Products covered
This guide covers the following products:
Part number
Model
MSM310 Access Point J9374A/B J9524A/B J9379A/B
MSM310-R Access Point J9380A/B J9383A/B
MSM317 Access Device J9422A J9423A J9423A
MSM320 Access Point J9360A/B J9527A/B J9364A/B
MSM320-R Access Point J9365A/B J9528A/B J9368A/B
MSM325 Access Point with Sensor J9369A/B J9373A/B
MSM335 Access Point with Sensor J9356A/B J9357A/B
MSM410 Access Point J9426A/B J9529A/B J9427A/B
MSM422 Access Point J9358A/B J9530A/B J9359A/B
USA Japan WW
Important terms
The following terms are used in this guide.
Ter m Description
AP Refers to any HP ProCurve Networking MSM3xx or MSM4xx
controller, service
controller
VSC, Virtual ap, VAP These terms are used interchangeably to refer to VSC (Virtual
1-2
Access Point.
Refers to any HP ProCurve Networking MSM7xx Controller,
including both Access Controller and Mobility Controller
variants.
Service Community).
Page 25
Typographical conventions
Command syntax
Command syntax is formatted in a monospaced font as follows:
Example Description
Introduction
New in this release
web admin kickout
ip http port <number>
end [force]
firewall mode
(high|low|none)
Items in plain text must be entered as shown.
Items in italics and enclosed in < > are parameters for
which you must supply a value. In this example, you
must supply a value for <number>.
Items enclosed in square brackets are optional. You
can either include them or not. Do not include the
brackets. In this example you can either include
“force” or omit it.
Items enclosed in parenthesis and separated by a
vertical line indicate a choice. Specify only one of the
items. In this example, you must specify ’high’, ’low’, or
’none’.
Management tool
When referring to the management tool interface, the Main menu name is presented first
followed by a right angle-bracket and then the sub-menu name, as in Network > Ports.
New in this release
New CLI commands in this release are identified by the text New in the left margin. This done
in both the table of contents, alphabetical list of commands, and Chapter 2: CLI commands.
HP ProCurve Networking support
The Customer Support/Warranty booklet included with your product and the HP ProCurve
Networking Web site, www.hp.com/go/procurve/support, provide information on the support
services offer by HP ProCurve Networking. Additionally, your HP-authorized network
reseller can provide you with assistance, both with services that they offer and with services
offered by HP.
1-3
Page 26
Introduction
Online documentation
Before contacting support
To make the support process most efficient, before calling your networking dealer or HP
Support, you first should collect the following information:
Collect this information Where to find it
Product identification. On the rear of the product.
Software version. The product management tool Login page.
Network topology map, including the
addresses assigned to all relevant devices.
Your network administrator.
Online documentation
For the latest documentation, visit the HP ProCurve Networking manuals Web page at:
www.hp.com/go/procurve/manuals.
CLI support in autonomous and controlled
modes
An AP operates in either controlled mode or autonomous mode.
Controlled mode
Controlled mode is the factory default mode for all APs.
When in controlled mode, an AP establishes a control channel with a controller. The
controller manages the AP and provides all configuration settings. Discovery of the controller
is automatic if default settings are used on all devices.
Note In controlled mode, access to the CLI is possible only before the control channel to the
controller is established, which can occur in the following scenarios:
Network failures prevent a control channel from being created.
After an AP is restarted, prior to establishment of the control channel (during the brief
controller discovery process).
When the AP is in controlled mode, a reduced number of CLI commands are available. The
most notable command is switch operational mode, which enables you to switch the AP to
autonomous mode. The config context is not available.
1-4
Page 27
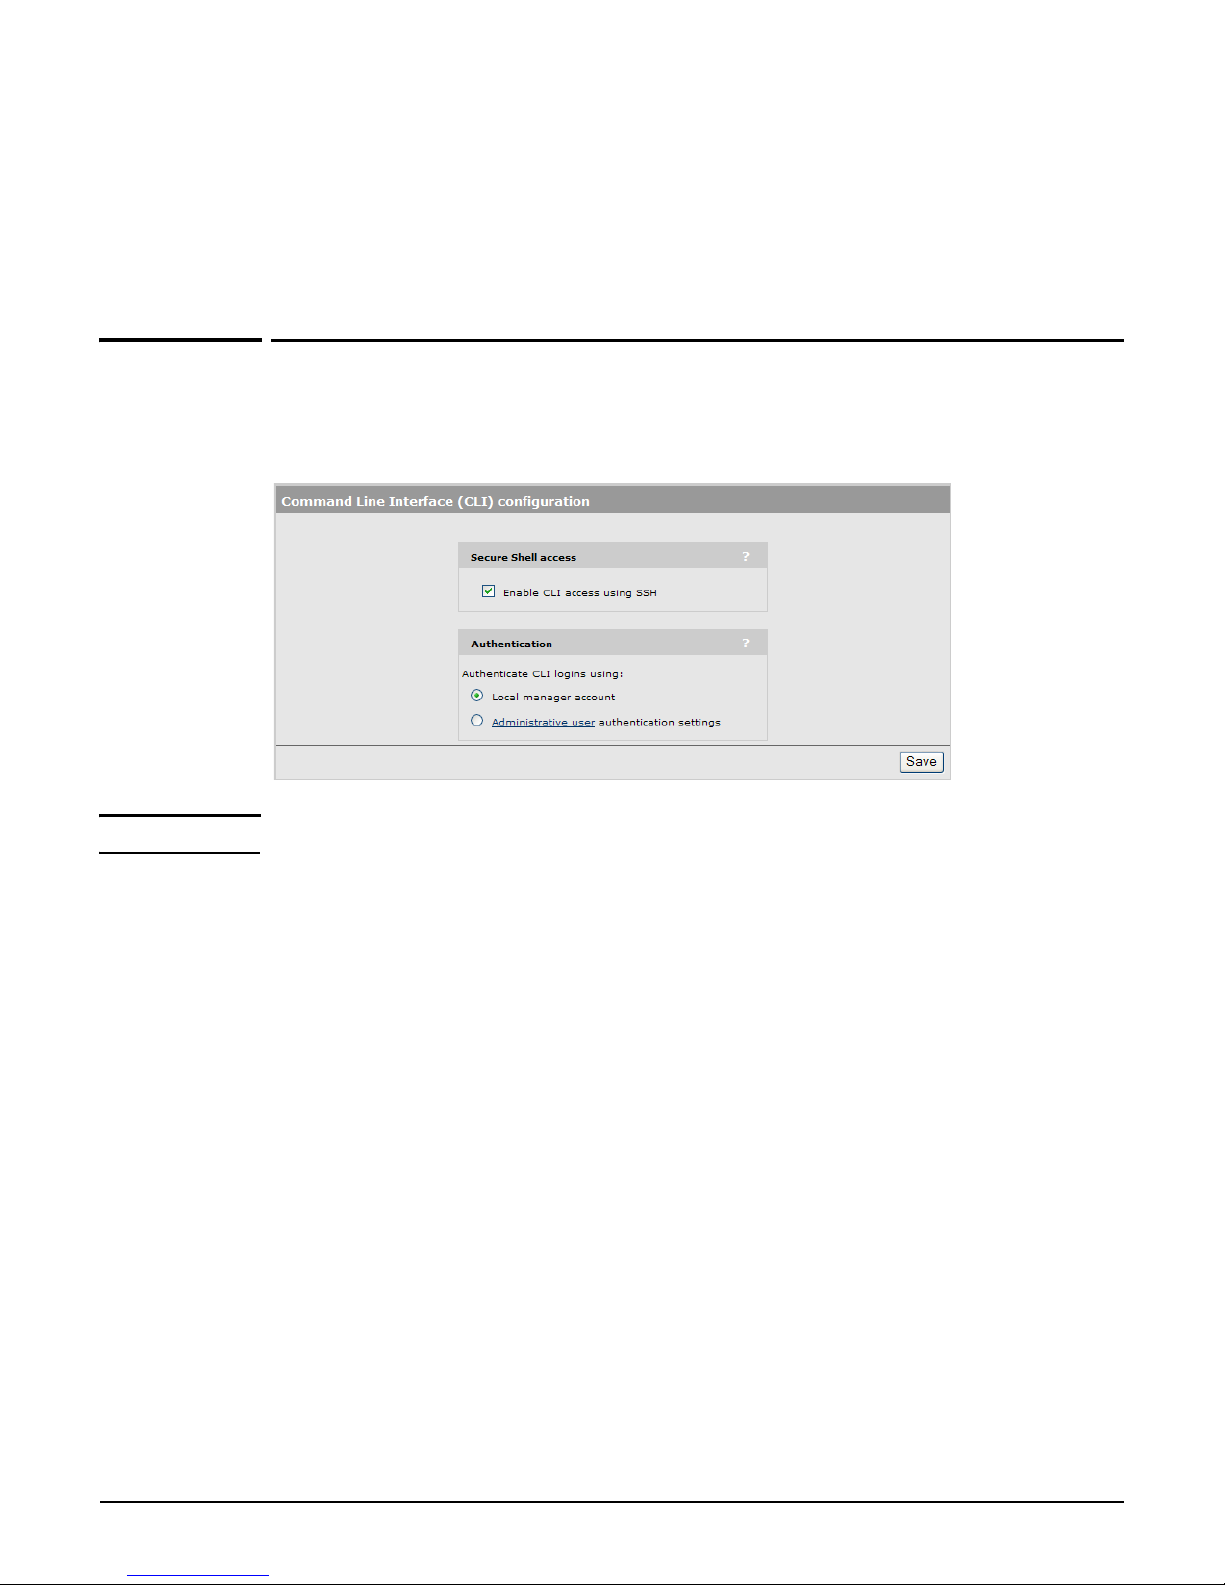
Introduction
Configuring CLI support
Autonomous mode
When in autonomous mode, the AP operates as a stand-alone unit. Autonomous mode
supports all CLI commands. You can also configure and manage the AP using the AP
management tool, SNMP, CLI, or SOAP.
Configuring CLI support
CLI support is configured using the management tool on the AP. Select Management > CLI
to open the Command Line Interface (CLI) configuration page.
Note A maximum of three concurrent CLI sessions are supported.
Secure shell access
Enable this option to allow access to the CLI via an SSH session. The CLI supports SSH on
the standard TCP port (22).
Connectivity and login credentials for SSH connections use the same settings as defined for
management tool on the Controller >> Management > Management tool page. SSH
connections to the CLI can be made on any active interface. Support for each interface must
be explicitly enabled under Security.
The following SSH clients have been tested with the CLI. Others may work as well:
OpenSSH
Tect ia
SecureCRT
Putty
Authenticate CLI logins using
The CLI validates login credentials (username and password) using the settings defined on
the Management > Management tool page. (Shown below for reference)
1-5
Page 28
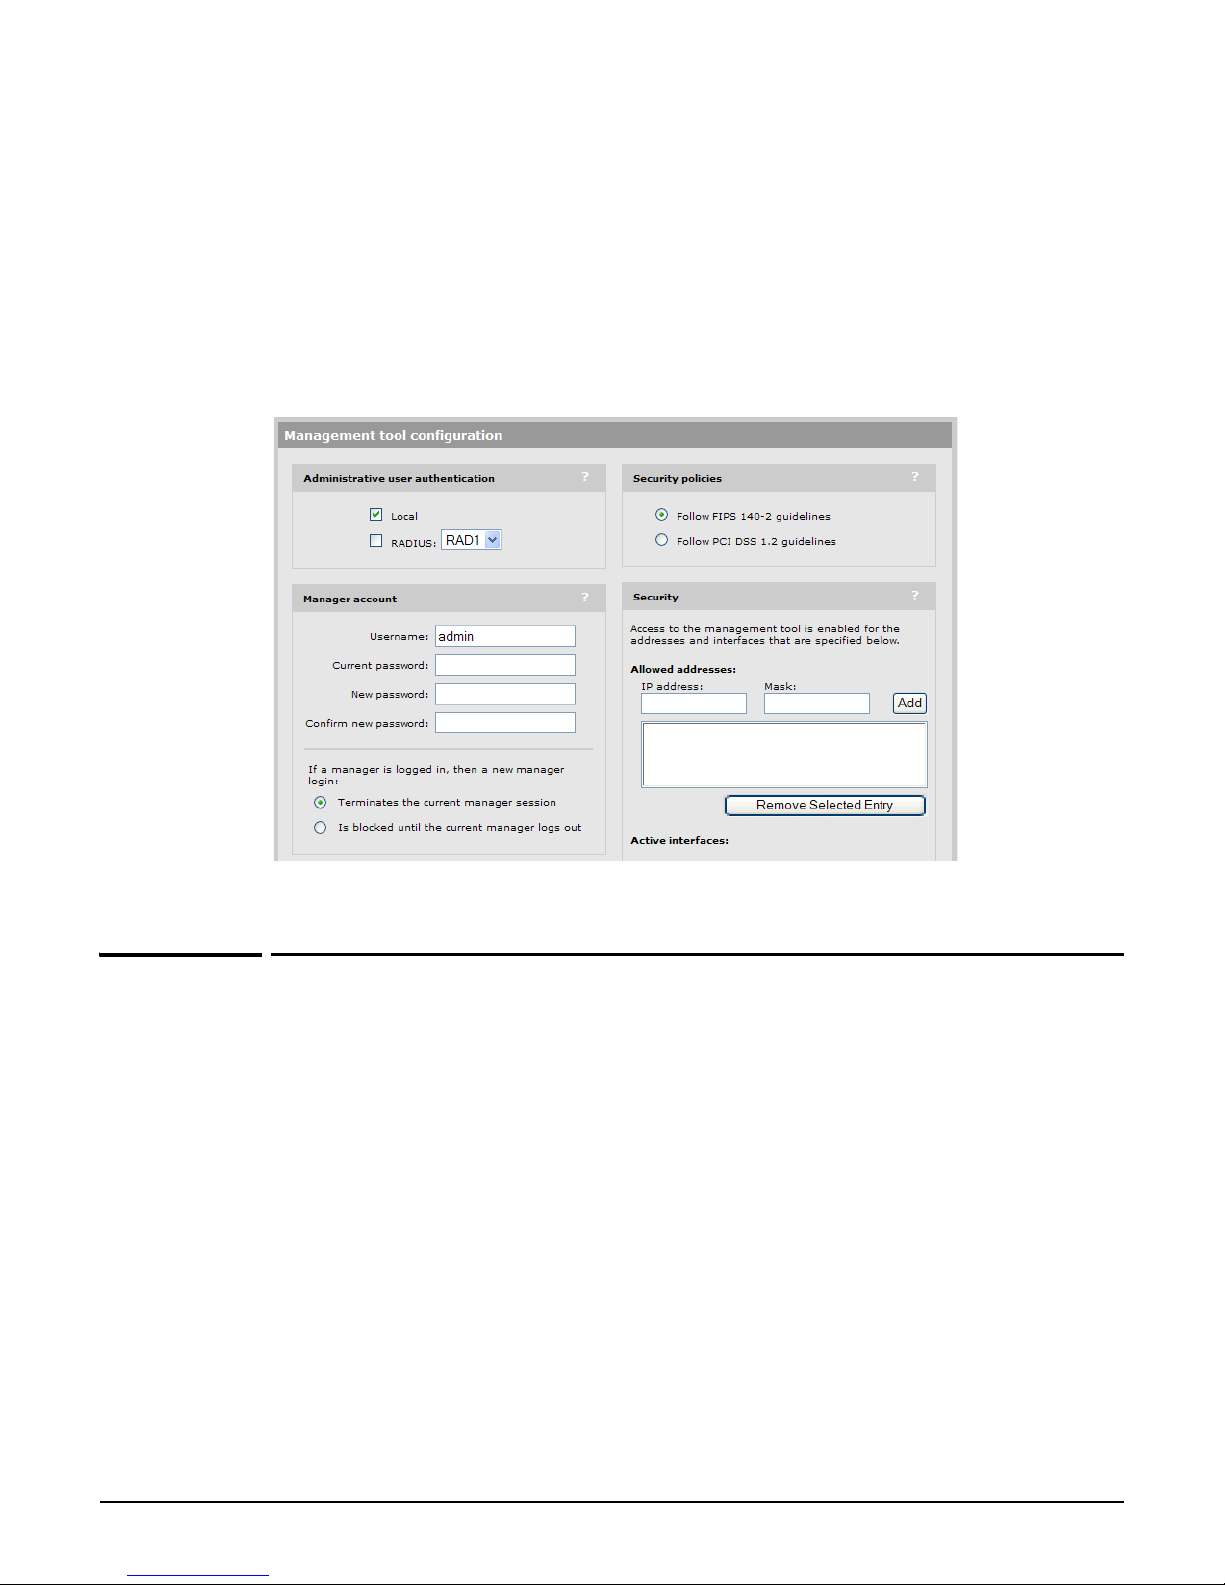
Introduction
Entering strings
Local manager account
The login username and password are the same as those defined for the local manager
account. If this account is disabled, the last known username and password for this account
are used.
Administrative user authentication settings
The login username and password use the same settings (Local and/or RADIUS) as defined
for the manager account under Administrative user authentication.
Entering strings
When entering a value that contains spaces, you must enclose it in quotation marks. For
example, if the command syntax is:
ssid <name>
you must specify one of the following:
ssid ANameWithNoSpaces
ssid "A name with spaces"
1-6
Page 29
Introduction
Context hierarchy
Context hierarchy
CLI commands are grouped into functional contexts. The following table shows the context
hierarchy and the command used to switch from the parent context.
Context hierarchy Command to switch from parent context
View context (This is the root context. No command is needed.)
Enable context enable
Config context config
WAN IP interface context interface ip
Port-2 interface context interface ethernet port-2
VLAN interface context interface vlan <id>[-<id2>]
Port-1 interface context interface ethernet port-1
VLAN interface context interface vlan <id>[-<id2>]
Wireless context interface wireless <number>
Local mesh context local mesh profile <name>
VLAN interface context interface vlan <number>
GRE interface context interface gre <name>
Virtual AP context virtual ap <name>
Syslog destination context logging destination <name>
SNMP user context snmp-server user <name>
SNMP notification receiver context snmp-server notification receiver <host>
RADIUS context radius-server profile <name>
IP_QOS context ip-qos profile <name>
Network profile context network-profile <name>
Sample CLI session
This sample CLI session shows you how to set the wireless port to support 802.11a on
channel 60 with medium distance between access points. (The CLI prompt is shown in bold.)
CLI> enable
CLI# config
CLI(config)# interface wireless
CLI(config-if-wlan)# dot11 a 60
CLI(config-if-wlan)# distance medium
CLI(config-if-wlan)# end
CLI(config)# end
CLI# quit
1-7
Page 30
Introduction
Sample CLI session
1-8
Page 31
Chapter 2: CLI commands
CLI commands
Contents
View context .................................................................................................................2-2
Enable context..............................................................................................................2-4
Config context ..............................................................................................................2-9
Port 2 port interface context ....................................................................................2-47
Port 1 port interface context ....................................................................................2-49
2
WAN IP interface context..........................................................................................2-51
Wireless context.........................................................................................................2-54
Virtual AP context......................................................................................................2-60
VLAN interface context .............................................................................................2-72
Local mesh context....................................................................................................2-73
RADIUS profiles context...........................................................................................2-78
IP QOS context ...........................................................................................................2-81
GRE interface context ...............................................................................................2-83
Syslog context ............................................................................................................2-84
SNMP user context ....................................................................................................2-87
SNMP notification receiver context ........................................................................2-88
Network profile context............................................................................................2-89
LLDP agent context ...................................................................................................2-90
Page 32
CLI commands
View context
View context
Path: View
This is the root of the command tree.
arping
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
arping [ -AbDfhqUV] [ -c <count>] [ -w <deadline>] [ -s <source>] -I <interface>
<destination>
Pings a destination on a device interface using ARP packets.
enable
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
enable
Switches to the enable context.
iperf
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
iperf -c host [-t time]
Runs a performance throughput test.
Parameters
<-c host> The IP address or DNS name of the iperf server to connect to.
<-t length> Length of the throughput test in seconds.
nslookup
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
nslookup [ -option authentication ] [ <host-to-find> | - [< server> ]]
Queries DNS servers for information on hosts or domains.
ping
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ping <host> [-c <count>] [-s <length>] [-q]
Determines if the specified remote IP address is active.
Parameters
<-c host> The IP address or DNS name of the host to ping.
<-c count> Number of pings.
<-s length> Length of the ping datagram.
<-q> Quiet mode. No output.
2-2
Page 33
ps
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ps
Displays all running processes.
quit
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
quit
Quits the CLI.
show license
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show license (eula | gpl | other)
Displays license information.
CLI commands
View context
show logging filtered
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show logging [filtered]
Displays the system log.
top
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
top
Displays all running processes.
traceroute
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
traceroute [-n] [-r] [-v] [-m <max_ttl>] [-p <port#>] [-q <nqueries>] [-s
<src_addr>] [-t <tos>] [-w <wait>] <host> [<data size>]
Show the hosts that are traversed to reach the specified IP address.
2-3
Page 34
CLI commands
Enable context
Enable context
Path: View > Enable
This context provides access to various utilities.
reboot device
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
reboot device
Restarts the system.
show certificate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show certificate
Displays current certificates.
show certificate binding
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show certificate binding
Displays how the certificates are used.
iperf
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
iperf -c host [-t time]
Runs a performance throughput test.
Parameters
<-c host> The IP address or DNS name of the iperf server to connect to.
<-t length> Length of the throughput test in seconds.
ping
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ping <host> [-c <count>] [-s <length>] [-q]
Determines if the specified remote IP address is active.
Parameters
<-c host> The IP address or DNS name of the host to ping.
<-c count> Number of pings.
<-s length> Length of the ping datagram.
<-q> Quiet mode. No output.
2-4
Page 35
CLI commands
Enable context
arping
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
arping [ -AbDfhqUV] [ -c <count>] [ -w <deadline>] [ -s <source>] -I <interface>
<destination>
Pings a destination on a device interface using ARP packets.
arp
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
arp [-evn] [-H <type>] [-i if] ?- [<hostname>] arp [-v] [-i if] -d <hostname>
[pub] arp [-v] [-H <type>] [-i if] -s <hostname> <hw_addr> [temp] arp [-v] [-H
<type>] [-i if] -s <hostname> <hw_addr> [<netmask> <nm>] <pub> arp [-v] [-H
<type>] [-i if] -Ds <hostname> ifa [<netmask> <nm>] <pub>
Displays and modifies the Internet-to-Ethernet address translation tables used by the address
resolution protocol.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
quit
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
quit
Exits the enable context.
rcapture
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
rcapture -u <URI> [-c <count>] -i <interface>
Captures data on a port and sends it to a file on an FTP server.
Parameters
<URI> Address of the FTP site and filename where the trace will be saved. For
example: ftp://user:[email protected]/trace.pcap
<count> Number of packets to capture.
<interface> Interface to trace: eth0 = Internet port, eth1 = LAN port, wvlan0 = wireless
port
show arp
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show arp
Shows the ARP table.
2-5
Page 36
CLI commands
Enable context
show bridge
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show bridge
Shows bridge information.
show bridge forwarding
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show bridge forwarding
Shows bridge forwarding information.
show dns cache
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show dns cache [<serial>]
Shows DNS cache entries. Specify a serial number to display detailed information.
show interfaces
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show interfaces
Show networking interfaces.
show ip
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show ip
Shows all IP addresses.
show ip route
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show ip route
Shows all IP routes.
show system info
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show system info
Shows basic system information.
New show wireless clients
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show wireless clients
Displays all wireless clients.
2-6
Page 37
New disassociate wireless client _
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
disassociate wireless client [<client_macaddress>]
Terminates the connection for the specified wireless client.
factory reset
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
factory reset
Resets the unit to factory default settings.
switch operational mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
switch operational mode
Switches the unit’s operational mode.
CLI commands
Enable context
show dot11 associations
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show dot11 associations
Shows all current wireless associations.
show dot11 statistics client-traffic dot11n
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show dot11 statistics client-traffic [dot11n [<macaddress]>]
Shows current client matrix statistics.
show local mesh
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show local mesh
Shows current local mesh interfaces.
show wireless neighborhood
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show wireless neighborhood
Shows all access points detected nearby.
show wireless rogue-ap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show wireless rogue-ap
Shows all rogue access points detected nearby.
2-7
Page 38
CLI commands
Enable context
show client log
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show client log [<macaddr>]
Displays the client station log. Enter the MAC address to display more details for a specific client
station.
show discrete pin
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show discrete pin
Displays the state of the discrete pin.
config
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config
Switches to the config context.
show all config
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show all config
Shows all configuration settings that apply to this device.
2-8
Page 39
CLI commands
Config context
Config context
Path: View > Enable > Config
This is the root context for all configuration commands.
certificate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
certificate (authority | local) <uri> <certname> [<password>]
Adds a new certificate to the store, using the specified friendly name.
certificate binding
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
certificate binding (web-management | html-auth | soap | eap) <certname>
Assigns a certificate to a service.
no certificate binding (web-management | html-auth | soap | eap) <certname>
Unassigns a certificate from a service.
certificate revocation
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
certificate revocation <uri> <certname>
Adds a Certificate Revocation List (CRL) to an existing authority certificate.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
factory settings
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
factory settings
Resets the system configuration to factory default settings.
interface ethernet
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface ethernet (port-1|port-2)
Switches to the specified Ethernet interface context.
2-9
Page 40
CLI commands
Config context
New network-profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
network-profile <name>
Add/Edits the specified network profile or create a new profile with the specified name.
no network-profile <name>
Deletes the network profile with the specified name.
reboot device
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
reboot device
Restarts the system.
show certificate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show certificate
Displays current certificates.
show certificate binding
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show certificate binding
Displays how the certificates are used.
show config factory
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show config [factory]
Generates a list of CLI commands that can be used to define the currently loaded configuration.
New show network-profiles
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show network-profiles
Displays all currently defined network profiles.
interface ip
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface ip
Switches to the specified IP interface context.
2-10
Page 41
interface wireless
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface wireless <interface number>
Switches to the specified wireless interface context.
local mesh profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
local mesh profile <name>
Switches to the specified local mesh link context.
Parameters
<name> Number of the local mesh profile to configure.
interface gre
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface gre <name>
CLI commands
Config context
Switches to the specified GRE interface or creates a new GRE interface with the specified name.
no interface gre <name>
Deletes the specified GRE interface.
virtual ap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
virtual ap <name>
Creates a new VSC (VAP) profile or switches to the existing VSC (VAP) context with the specified
name.
no virtual ap <name>
Deletes the specified VSC (VAP) profile.
Parameters
name Name of an existing or new VSC (VAP) profile.
cap-switch to
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
cap-switch to (ap | ac | wab)
Switches to the specified operational mode.
Parameters
ap Switches operational mode to CAP MultiService Access Point.
ac Switches operational mode to CAP MultiService Controller.
wab Switches operational mode to WAB Wireless Station.
2-11
Page 42
CLI commands
Config context
admin local authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
admin local authentication
Sets the authentication of manager logins to occur using the local account.
no admin local authentication
Disables administrator authentication via the local account.
admin radius authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
admin radius authentication
Sets the authentication of manager logins to occur using RADIUS.
no admin radius authentication
Disables manager authentication via RADIUS.
admin radius authentication server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
admin radius authentication server <name>
Sets the authentication of manager logins to occur using RADIUS.
ip http port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip http port <number>
Sets the port number to use for HTTP access to the AP.
Parameters
<number> Port number. Range: 1 - 65535.
Description
HTTP connections made to this port are met with a warning and the browser is redirected to the
secure web server port. By default. this parameter is set to port 80.
ip https port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip https port <number>
Sets the port number used for HTTPS access to the AP.
Parameters
<number> Port number. Range: 1 - 65535.
snmp-server trap certificate-expired
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap certificate-expired
Send a trap when the SSL certificate has expired. A trap is sent every 12 hours.
2-12
Page 43
CLI commands
Config context
no snmp-server trap certificate-expired
Do not send a trap when the SSL certificate has expired.
snmp-server trap certificate-expires-soon
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap certificate-expires-soon
Send a trap when the SSL certificate is about to expire. A trap is sent every 12 hours starting 15
days before the certificate expires.
no snmp-server trap certificate-expires-soon
Do not send a trap when the SSL certificate is about to expire.
snmp-server trap web-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap web-fail
Send a trap each time an manager login is refused.
no snmp-server trap web-fail
Do not send a trap each time an manager login is refused.
snmp-server trap web-login
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap web-login
Send a trap each time an manager login is accepted.
no snmp-server trap web-login
Do not send a trap each time an manager login is accepted.
snmp-server trap web-logout
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap web-logout
Send a trap each time an manager logs out.
no snmp-server trap web-logout
Do not send a trap each time an manager logs out.
username
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
username <user> <password>
Changes the current manager local username and password.
Parameters
<user> New manager username.
2-13
Page 44
CLI commands
Config context
<password> New manager password. New password must be between 6 and 16
printable characters in length and contain at least 4 different characters.
Passwords are case sensitive. Space characters and double quotes cannot
be used. Passwords must also conform to the Security policy that is in
effect.
web admin kickout
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web admin kickout
Enables a new manager login to terminate an existing manager session.
no web admin kickout
Stops a new manager from logging in until an existing manager logs out.
web allow
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web allow <ip address>/<mask>
Adds an address to the list of hosts that can access the management tool.
no web allow <ip address>/<mask>
Removes the specified address from the list of hosts that can access the management tool.
Parameters
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
world-mode dot11 country code
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
world-mode dot11 country code <code>
Specifies the country in which the AP is operating.
Parameters
<code> An ISO3166 three-letter country code.
web access port-1
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web access port-1
Enables access to the management tool via Port 2.
no web access port-1
Blocks access to the management tool via Port 2.
web access port-2
Supported on: MSM320 MSM310
web access port-2
Enables access to the management tool via Port 1.
2-14
Page 45
no web access port-2
Blocks access to the management tool via Port 1.
web access wireless
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web access wireless
Enables access to the management tool via the wireless port.
no web access wireless
Blocks access to the management tool via the wireless port.
web access interface vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web access interface vlan <name>
Enables access to the management tool via the specified VLAN.
no web access interface vlan <name>
CLI commands
Config context
Removes access to the management tool for the specified VLAN.
web access interface gre
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web access interface gre <name>
Enables access to the management tool via the specified GRE tunnel.
no web access interface gre <name>
Disables access to the management tool via the specified GRE tunnel.
web access local mesh
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
web access local mesh <name>
Enables access to the management tool via the specified local mesh link.
no web access local mesh <name>
Disables access to the management tool via the specified local mesh link.
New console authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
console authentication (always-local | like-web)
Sets how logins to the CLI are authenticated.
Parameters
<always-local> The login username and password are the same as those defined for the
local manager account. If this account is disabled, the last known
username and password for this account are used.
2-15
Page 46
CLI commands
Config context
<like-web> The login username and password use the same settings (Local and/or
RADIUS) as defined for the manager account in the web interface.
clock
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock <time> <date>
Sets the system time and date.
Parameters
<time> Time as hh:mm:ss. For example: 15:44:00.
<date> Date as dd mmm yyyy. For example: 17 Oct 2004
clock auto adjust dst
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock auto adjust dst
Automatically adjust clock for daylight savings changes.
no clock auto adjust dst
Do not automatically adjust clock for daylight savings changes.
clock timezone
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock timezone <gmtdiff>
Sets the time zone the AP is operating in.
Parameters
<gmtdiff> Offset from GMT as follows: +-HOUR:MIN. For example, Eastern Standard
time is -5:00.
clock use custom dst rules
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock use custom dst rules
Use custom DST rules instead of default ones.
no clock use custom dst rules
Do not use custom DST rules, use default ones.
ntp protocol
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ntp protocol (ntp | sntp)
Sets the network time protocol to use.
2-16
Page 47
CLI commands
Config context
ntp server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ntp server
Enable this option to have the AP periodically contact a network time server to update its internal
clock.
no ntp server
Disables the use of a network time server.
clock custom dst begins
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock custom dst begins <day> <weekday> <month> <time>
Set parameters of the rule defining the beginning of daylight savings time.
Parameters
<day> Day of the month. Range 1 - 31.
<weekday> Weekday. Valid values are: "sun", "mon", "tue", "wed", "thu", "fri", "sat".
<month> Month. Valid values are: "jan", "feb", "mar", "apr", "may", "jun", "jul", "aug",
"sep", "oct", "nov", "dec".
<time> Time as hh:mm[:ss]. For example: 15:44:00.
If a parameter does not apply to the configured DST rule format, simply set this parameter to any
valid value.
clock custom dst begins format
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock custom dst begins format (<fixed>|<last-weekday>|<followingdate>|<preceding-date>
Set the format of the custom DST rule.
Parameters
<fixed> Rule of the form: The [Day]th of [Month] at [Time].
<last-weekday> Rule of the form: The last [Weekday] of [Month] at [Time].
<following-date> Rule of the form: The first [Weekday] on or after the [Day]th of [Month] at
[Time].
<preceding-date> Rule of the form: The first [Weekday] on or before the [Day]th of [Month]
at [Time].
clock custom dst ends
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock custom dst ends <day> <weekday> <month> <time>
Set parameters of the rule defining the end of daylight savings time.
Parameters
<day> Day of the month. Range 1 - 31.
<weekday> Weekday. Valid values are: "sun", "mon", "tue", "wed", "thu", "fri", "sat".
2-17
Page 48
CLI commands
Config context
<month> Month. Valid values are: "jan", "feb", "mar", "apr", "may", "jun", "jul", "aug",
"sep", "oct", "nov", "dec".
<time> Time as hh:mm[:ss]. For example: 15:44:00.
If a parameter does not apply to the configured DST rule format, simply set this parameter to any
valid value.
clock custom dst ends format
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
clock custom dst ends format (<fixed>|<last-weekday>|<followingdate>|<preceding-date>
Set the format of the custom DST rule.
Parameters
<fixed> Rule of the form: The [Day]th of [Month] at [Time].
<last-weekday> Rule of the form: The last [Weekday] of [Month] at [Time].
<following-date> Rule of the form: The first [Weekday] on or after the [Day]th of [Month] at
[Time].
<preceding-date> Rule of the form: The first [Weekday] on or before the [Day]th of [Month]
at [Time].
ntp server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ntp server <index><host>
Adds the specified network time server.
Parameters
<index> Index of the time server in the list. Up to 20 time servers are supported.
Time servers are checked in the order that they appear in the list.
<host> DNS name or IP address of the time server.
ntp server failure trap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ntp server failure trap
Send a trap each time a time server synchronization failed.
no ntp server failure trap
Do not send a trap each time a time server synchronization failed.
config-update automatic
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update automatic
Enables scheduled configuration restore or backup.
no config-update automatic
Disables scheduled configuration restore or backup.
2-18
Page 49
The AP can automatically download the configuration file from a local or remote URL (restore). It
is also possible to upload the current configuration to a given URL (backup). Theses operations
can be done at preset times.
config-update operation
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update operation (restore | backup)
Sets the type of operation that will take place at the preset time.
New config-update start
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update start
Start a config update now. Will reboot on success.
config-update time
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update time <time>
CLI commands
Config context
Sets the time of day when the scheduled configuration operation (backup or restore) will take
place.
Parameters
<time> Time as hh:mm:ss. For example: 15:44:00.
config-update uri
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update uri <uri>
Sets the URI where the AP will download or upload the configuration file.
no config-update uri
Clears the configuration file URI.
config-update weekday
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-update weekday (everyday | monday | tuesday | wednesday | thursday |
friday | saturday | sunday)
Sets the day when the scheduled configuration operation (backup or restore) will take place.
snmp-server trap config-change
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap config-change
Send a trap whenever the configuration is changed.
no snmp-server trap config-change
Do not send this trap.
2-19
Page 50
CLI commands
Config context
snmp-server trap config-update
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap config-update
Send a trap whenever the firmware is updated.
no snmp-server trap config-update
Do not send this trap.
logging destination
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
logging destination <name>
Creates a new remote destination for syslog.
no logging destination <name>
Deletes the specified syslog destination.
Parameters
<name> Name of syslog destination. Use the name "local" to edit your local log file
settings. Any other name will edit/create a remote log destination.
snmp-server trap syslog-severity
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap syslog-severity
Set the severity level of syslog messages that will trigger a trap.
no snmp-server trap syslog-severity
Do not send this trap.
snmp-server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server
Enables the SNMP agent.
no snmp-server
Disables the SNMP agent.
snmp-server access port-1
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server access port-1
Enables SNMP access on the downstream port.
no snmp-server access port-1
Blocks SNMP access on the downstream port.
2-20
Page 51
CLI commands
Config context
snmp-server allow
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server allow <ip address>/<mask>
Adds a host to the list of IP address from which access to the SNMP interface is permitted.
no snmp-server allow <ip address>/<mask>
Removes a host from the list of IP address from which access to the SNMP interface is permitted.
Parameters
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
snmp-server chassis-id
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server chassis-id <name>
Specifies a name to identify the AP. By default, this is set to the serial number of the AP.
no snmp-server chassis-id
Deletes the system name.
snmp-server contact
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server contact <email>
Specifies contact information.
no snmp-server contact
Deletes contact information.
Parameters
<email> Email address.
snmp-server heartbeat period
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server heartbeat period <seconds>
Sets the interval between sending heartbeat traps.
Parameters
<seconds> Heartbeat interval in seconds.
snmp-server location
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server location <name>
Specifies the location where the AP is installed.
no snmp-server location
Deletes location information.
2-21
Page 52
CLI commands
Config context
Parameters
<name> Location where the AP is installed.
snmp-server port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server port <port number>
Sets the port the AP will use to respond to SNMP requests.
Parameters
<port number> SNMP port number. Range 1 - 65535.
snmp-server readonly
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server readonly <community>
Sets the read-only community string.
no snmp-server readonly
Deletes the read-only community string.
snmp-server readwrite
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server readwrite <community>
Sets the read-write community string.
no snmp-server readwrite
Deletes the read-write community string.
snmp-server trap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap
Enables support for SNMP traps.
no snmp-server trap
Disables support for SNMP traps.
snmp-server trap community
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap community <str>
Sets the password required by the remote host that will receive the trap.
no snmp-server trap community
Deletes the password required by the remote host that will receive the trap.
2-22
Page 53
CLI commands
Config context
snmp-server trap destination
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap destination <host> <[port number]>
Add a new trap destination.
no snmp-server trap destination <host> [<port>]
Deletes the specified trap destination.
Parameters
<host> Sets the IP address or domain name of the host that the AP will send traps
to.
<[port number]> SNMP port number. Range 1 - 65535. By default port 162 is used
snmp-server trap heartbeat
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap heartbeat
Enables sending of heartbeat traps at regular intervals.
no snmp-server trap heartbeat
Disables sending of heartbeat traps at regular intervals.
snmp-server trap link-state
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap link-state
Send a trap when the link state changes on any interface.
no snmp-server trap link-state
Do not send this trap.
snmp-server trap snmp-authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap snmp-authentication
Send a trap each time an SNMP request fails to supply the correct community name.
snmp-server version 1
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server version 1
Enable support for SNMP version 1.
no snmp-server version 1
Disable support for SNMP version 1.
2-23
Page 54
CLI commands
Config context
snmp-server version 2c
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server version 2c
Enable support for SNMP version 2c.
no snmp-server version 2c
Disable support for SNMP version 2c.
snmp-server version 3
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server version 3
Enable support for SNMP version 3.
no snmp-server version 3
Disable support for SNMP version 3.
snmp-server access interface vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server access interface vlan <name>
Enables access to SNMP via the specified VLAN.
no snmp-server access interface vlan <name>
Disables access to SNMP via the specified VLAN.
Parameters
<name> Specifies the name of the VLAN.
snmp-server access local mesh
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server access local mesh <profile>
Enables access to SNMP via the specified local mesh.
no snmp-server access local mesh <profile>
Enables access to SNMP via the specified local mesh.
snmp-server access interface gre
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server access interface gre <name>
Enables access to SNMP via the specified GRE tunnel.
no snmp-server access interface gre <name>
Removes access to SNMP via the specified GRE tunnel.
2-24
Page 55
snmp-server access wireless
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server access wireless
Enables SNMP access on the wireless port.
no snmp-server access wireless
Blocks SNMP access on the wireless port.
snmp-server access port-2
Supported on: MSM320 MSM310
snmp-server access port-2
Enables SNMP access on the upstream port.
no snmp-server access port-2
Blocks SNMP access on the upstream port.
snmp-server user
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server user <name>
CLI commands
Config context
Creates a new SNMP user or switches to the SNMP user context with the specified user name.
no snmp-server user <name>
Deletes the specified SNMP user.
snmp-server notification receiver
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server notification receiver <host>
Creates a new SNMP notification receiver or switches to the SNMP notification receiver context
with the specified IP address.
no snmp-server notification receiver <host>
Deletes the specified SNMP notification receiver.
soap-server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server
Enables the SOAP server.
no soap-server
Disables the SOAP server.
2-25
Page 56
CLI commands
Config context
soap-server access interface vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access interface vlan <name>
Enables access to SOAP via this VLAN.
no soap-server access interface vlan <name>
Disables access to SOAP via this VLAN.
soap-server access port-1
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access port-1
Enables SOAP access on the downstream port.
no soap-server access port-1
Blocks SOAP access on the downstream port.
soap-server access port-2
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access port-2
Enables SOAP access on the upstream port.
no soap-server access port-2
Blocks SOAP access on the upstream port.
soap-server allow
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server allow <ip address>/<mask>
Adds a host to the list of IP addresses from which access to the SOAP interface is permitted.
no soap-server allow <ip address>/<mask>
Removes a host from the list of IP addresses from which access to the SOAP interface is
permitted.
Parameters
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
soap-server http authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server http authentication
Enable the SOAP server HTTP authentication.
no soap-server http authentication
Disable the SOAP server HTTP authentication.
2-26
Page 57
soap-server http authentication password
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server http authentication password
Set the SOAP server HTTP authentication password.
soap-server http authentication username
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server http authentication username
Set the SOAP server HTTP authentication username.
soap-server port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server port <port number>
Sets the port the AP will use to respond to SOAP requests.
Parameters
<port number> SOAP port number. Range 1 - 65535.
CLI commands
Config context
soap-server ssl
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server ssl
SSL enabled for SOAP server.
no soap-server ssl
SSL disabled for SOAP server.
soap-server ssl with client certificate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server ssl with client certificate
Enable the use of client certificate with SSL for SOAP server.
no soap-server ssl with client certificate
Disable the use of client certificate with SSL for SOAP server.
soap-server access interface gre
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access interface gre <name>
Enables access to SOAP via the specified GRE tunnel.
no soap-server access interface gre <name>
Removes access to SOAP via the specified GRE tunnel.
2-27
Page 58
CLI commands
Config context
soap-server access wireless
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access wireless
Enables SOAP access on the wireless port.
no soap-server access wireless
Blocks SOAP access on the wireless port.
soap-server access local mesh
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
soap-server access local mesh <profile>
Enables access to the management tool via the specified local mesh link.
no soap-server access local mesh <profile>
Disables access to the management tool via the specified local mesh link.
snmp-server trap low-snr
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap low-snr
Send a trap when the average signal to noise ratio on a VAP (VSC) exceeds a specified level.
no snmp-server trap low-snr
Do not send this trap.
snmp-server trap low-snr interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap low-snr interval <number>
Sets the interval at which the average SNR level is checked for each VAP (VSC).
snmp-server trap low-snr level
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap low-snr level <number>
Sets the SNR level that will trigger a trap.
snmp-server trap new-association
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap new-association
Send trap on when a new wireless client station associates with any VAP (VSC).
no snmp-server trap new-association
Do not send this trap.
2-28
Page 59
snmp-server trap new-association interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap new-association interval <number>
Interval, in minutes, between notifications.
snmp-server trap vpn-connection
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap vpn-connection
Send a trap when a user establishes a VPN connection with the AP.
no snmp-server trap vpn-connection
Do not send this trap.
snmp-server trap wireless-association-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-association-fail
CLI commands
Config context
Send a trap when a wireless client station fails to associate with the AP.
no snmp-server trap wireless-association-fail
Do not send this trap.
snmp-server trap wireless-association-success
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-association-success
Send a trap when a wireless client station successfully associates with the AP.
no snmp-server trap wireless-association-success
Do not send this trap.
snmp-server trap wireless-authentication-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-authentication-fail
Send a trap when a wireless client station fails to authenticate.
no snmp-server trap wireless-authentication-fail
Do not send this trap.
snmp-server trap wireless-authentication-success
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-authentication-success
Send a trap when a wireless client station is successfully associated.
no snmp-server trap wireless-authentication-success
Do not send this trap.
2-29
Page 60
CLI commands
Config context
snmp-server trap wireless-deauthentication-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-deauthentication-fail
Send a trap when a wireless client station fails to deauthenticate from the AP.
no snmp-server trap wireless-deauthentication-fail
Do not send this trap.
snmp-server trap wireless-deauthentication-success
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-deauthentication-success
Send a trap when a wireless client station deauthenticates from the AP.
no snmp-server trap wireless-deauthentication-success
Do not send this trap.
snmp-server trap wireless-disassociation-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-disassociation-fail
Send a trap when a wireless client station fails to disassociate from the AP.
no snmp-server trap wireless-disassociation-fail
Do not send this trap.
snmp-server trap wireless-disassociation-success
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-disassociation-success
Send a trap when a wireless client station disassociates from the AP.
no snmp-server trap wireless-disassociation-success
Do not send this trap.
snmp-server trap wireless-reassociation-fail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-reassociation-fail
Send a trap when a wireless client station fails to reassociate with the AP.
no snmp-server trap wireless-reassociation-fail
Do not send this trap.
snmp-server trap wireless-reassociation-success
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap wireless-reassociation-success
Send a trap when a wireless client station reassociates with the AP.
2-30
Page 61
no snmp-server trap wireless-reassociation-success
Do not send this trap.
snmp-server trap syslog-matches
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap syslog-matches
Send a trap when syslog messages matches a specified regular expression.
no snmp-server trap syslog-matches
Do not send this trap.
snmp-server trap syslog-matches regex
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap syslog-matches regex <regex>
Sets the regular expression used to match the syslog messages.
CLI commands
Config context
snmp-server trap syslog-severity level
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap syslog-severity level (debug | info | notice | warning | error
| critical | alert | emergency)
Set the severity level of syslog messages that will trigger a trap.
snmp-server trap network-trace
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap network-trace
Send a trap when a network trace is started or stopped.
no snmp-server trap network-trace
Do not send this trap.
firmware-update automatic
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
firmware-update automatic
Enables scheduled firmware upgrades.
no firmware-update automatic
Disables scheduled firmware upgrade.
The AP can automatically retrieve and install firmware from a local or remote URL at preset
times. By placing AP firmware on a web or ftp server, you can automate the update process for
multiple units.
When the update process is triggered the AP retrieves the first 2K of the firmware file to determine
if it is different from the active version. If different, the entire firmware file is then downloaded
and installed.
2-31
Page 62
CLI commands
Config context
(Different means older or newer. This enables you to return to a previous firmware version if
required).
Configuration settings are preserved during the update unless stated otherwise in the release
notes for the firmware. However, all active connections will be terminated. Customers will have to
log in again after the AP restarts
firmware-update start
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
firmware-update start
Upload the firmware based on a specified URI. This URI can be set with the command: firmwareupdate uri.
firmware-update time
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
firmware-update time <time>
Sets the time of day the scheduled firmware upgrade will take place.
Parameters
<time> Time as hh:mm:ss. For example: 15:44:00.
firmware-update uri
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
firmware-update uri <uri>
Sets the URI where the AP will retrieve new firmware.
no firmware-update uri
Clears the firmware URI.
firmware-update weekday
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
firmware-update weekday (everyday | monday | tuesday | wednesday | thursday |
friday | saturday | sunday)
Sets the day when the scheduled firmware upgrade will take place.
snmp-server trap firmware-update
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap firmware-update
Send a trap on firmware update.
no snmp-server trap firmware-update
Do not send a trap on firmware update.
2-32
Page 63
CLI commands
Config context
access-controller restrict location
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
access-controller restrict location (gateway | mac <mac address>)
Identifies the access controller the AP will communicate with.
Parameters
gateway Use the default gateway as the access controller.
mac Use the specified MAC address as the gateway.
<mac address> MAC address. Specify 6 pairs of hexadecimal numbers separated by
colons, with the values a to f in lowercase. For example: 00:00:00:0a:0f:01
service-sensor
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service-sensor
Enables the service sensor. The service sensor polls a target device at present intervals. If the
device does not respond, the radio is shut off.
no service-sensor
Disables the service sensor.
service-sensor
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service-sensor (gateway | address<ip address>)
Sets the target device the service sensor will poll. This can be the default gateway or a specific IP
address.
no service-sensor
Disables the service sensor.
Parameters
gateway The service sensor will poll the default gateway.
address The service sensor will poll another device.
<ip address> IP address of the other device. For example: 192.168.10.10
service-sensor poll
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service-sensor poll <seconds>
Sets the poll frequency.
Parameters
<seconds> Poll frequency. Range: 1 - 3600 seconds.
2-33
Page 64
CLI commands
Config context
service-sensor retry
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service-sensor retry <retries>
Specify how many retries the service sensor will attempt when polling the target device.
When the retry limit is reached, the radio on the AP is turned off.
Parameters
<retires> Number of retries. Range: 0 - 100.
service-sensor timeout
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service-sensor timeout <seconds>
Sets how long the service sensor will wait for a response to a poll before timing out.
Parameters
<seconds> Length of timeout. Range: 1 - 5 seconds.
ip name-server
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server <primary> [<secondary>] [<third>]
Sets the primary and secondary DNS servers overriding dynamically assigned ones.
Parameters
<primary> IP address of the primary DNS server.
<secondary> IP address of the secondary DNS server.
<third> IP address of the third DNS server.
ip name-server cache
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server cache
Enables the DNS cache.
no ip name-server cache
Disables the DNS cache.
Once a host name has been successfully resolved to an IP address by a remote DNS server, it is
stored in the cache. This speeds up network performance, as the remote DNS server now does not
have to be queried for subsequent requests for this host.
The entry stays in the cache until:
an error occurs when connecting to the remote host
the time to live (TTL) of the DNS request expires
the AP is restarted
2-34
Page 65
ip name-server dynamic
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server dynamic
Enables dynamic assignment of DNS servers.
no ip name-server dynamic
Disables dynamic DNS assignment.
New ip name-server interception
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server interception
Intercept all DNS requests from users and relay them to configured servers.
no ip name-server interception
Process DNS requests addressed to this device only.
ip name-server switch-on-servfail
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server switch-on-servfail
CLI commands
Config context
Switch to next server when server failure is received.
no ip name-server switch-on-servfail
Do not switch to next server when server failure is received.
ip name-server switch-over
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip name-server switch-over
Switch over to primary when active.
no ip name-server switch-over
Do not switch over to primary when active.
snmp-server trap unauthorized-ap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap unauthorized-ap
Send a trap when a rogue access point is detected.
no snmp-server trap unauthorized-ap
Do not send this trap.
2-35
Page 66
CLI commands
Config context
snmp-server trap unauthorized-ap interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
snmp-server trap unauthorized-ap interval <number>
If set to 0, then traps are only sent when a rogue access point is detected. If set to >0, the entire list
of rogue access points is sent each time the interval expires.
wireless-scan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless-scan
Enables wireless neighborhood scanning.
no wireless-scan
Disables wireless neighborhood scanning.
wireless-scan period
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless-scan period <seconds>
Specifies the interval between wireless neighborhood scans.
Parameters
<seconds> Scanning interval. Range: 10 - 600 seconds.
wireless-scan url
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless-scan url <location>
Sets the URL of the file that contains a list of all authorized access points.
no wireless-scan url
Deletes the URL of the file that contains a list of all authorized access points.
The format of this file is XML. Each entry in the file is composed of two items: MAC address and
SSID. Each entry should appear on a new line.
For example:
00:00:00:07:f5:11 "AP_1"
00:00:00:07:f5:23 "AP_2"
00:00:00:07:f5:12 "AP_3"
access controller shared secret
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
access controller shared secret <secret>
Sets the shared secret used to communicate with the controller.
no access controller shared secret
Sets the shared secret used to communicate with the access controller.
2-36
Page 67
CLI commands
Config context
The controller will only accept authentication/location-aware information from HP APs that have
a matching shared secret to its own.
radius-server profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
radius-server profile <name>
Creates a new RADIUS profile or switches to the RADIUS context with the specified profile name.
no radius-server profile <name>
Deletes the specified RADIUS profile.
ip-qos profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip-qos profile <name>
Creates a new IP QoS profile or switches to the IP QoS context with the specified profile name.
no ip-qos profile <name>
Deletes the specified IP QoS profile.
dot11 igmp snooping-helper
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 igmp snooping-helper
Enables IGMP snooping helpers which ensure that the AP correctly delivers multicast packets to
roaming client stations that are part of a multicast group.
no dot11 igmp snooping-helper
Disables IGMP snooping helpers.
New lldp config
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp config <port>
Edit LLPD port specific options.
New lldp dynamic-name
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp dynamic-name
Enables the LLDP dynamic naming feature.
no lldp dynamic-name
Disables the LLDP dynamic naming feature.
2-37
Page 68
CLI commands
Config context
New lldp dynamic-name refresh-time
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp dynamic-name refresh-time <time>
Sets the interval at which dynamic names for controlled APs are updated.
New lldp dynamic-name user-string
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp dynamic-name user-string <name>
Specifies the text to use for the dynamic name.
You can use regular text in combination with placeholders to create the name. Placeholders are
automatically expanded each time the name is regenerated.
Placeholders
%RN System name of the neighboring device to which the port is connected,
obtained via the System Name TLV. Since this is an optional TLV, if it is not
available, the Chassis ID TLV is used instead.
%RP Port description of the port on the neighboring device to which the local
port is connected, obtained via the Port Description TLV. Since this is an
optional TLV, if it is not available, the Port ID TLV is used instead.
%SN Controller’s serial number.
%IP Controller’s IP address. An IP address can require up to 15 characters
(nnn.nnn.nnn.nnn).
New lldp fast-start-count
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp fast-start-count <count>
After an MED LLDPDU is received, this timer is started and the agent sends one MED LLDPDU to
the MED device each second as it counts down.
New lldp holdtime-multiplier
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp holdtime-multiplier <hold>
Sets the hold time multiplier for LLDPDU transmissions.
The value of Multiplier is multiplied by the refresh-interval to define Time to live. Time to live
indicates the length of time that neighbors will consider LLDP information sent by this agent to be
valid.
New lldp med-location civic-address-element
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp med-location civic-address-element <caelement>
Adds a Civic Address Element.
2-38
Page 69
New lldp med-location elin-addr
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp med-location elin-addr <elin>
Sets the Emergency Call Services ELIN as described, for example, by NENA TID 07-501.
New lldp refresh-interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp refresh-interval <time>
Sets the interval (in seconds) at which local LLDP information is updated and TLVs are sent to
neighboring network devices.
New lldp run
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp run
Enables the LLDP Agent.
CLI commands
Config context
no lldp run
Disables the LLDP Agent.
New show lldp config
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show lldp config [<port>]
Shows LLDP configuration settings.
New show lldp info local-device
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show lldp info local-device [<port>]
Shows LLDP configuration settings.
New show lldp info remote-device
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show lldp info remote-device [<port>]
Shows LLDP configuration settings.
New show lldp stats
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show lldp stats [<port>]
Shows LLDP statistics for all ports or a specific port .
2-39
Page 70
CLI commands
Config context
New lldp local-mesh
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
lldp local-mesh
Enable LLDP support on local mesh links.
no lldp local-mesh
Disable LLDP support on local mesh links.
discovery protocol
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
discovery protocol
Enables broadcast of HP device information for interoperability with CDP-enabled networking
hardware.
no discovery protocol
Disable broadcast of HP device information.
discovery protocol device-id
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
discovery protocol device-id <name>
Overwrite the device-id field of information packets (the AP serial number is not used).
no discovery protocol device-id
Do not overwrite the device-id field of information packets (use the AP serial number).
New service controller discovery interface internet-port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service controller discovery interface internet-port
Allow discovery on the LAN port.
no service controller discovery interface internet-port
Allow discovery on the LAN port.
New service controller discovery interface lan-port
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
service controller discovery interface lan-port
Allow discovery on the LAN port.
no service controller discovery interface lan-port
Allow discovery on the LAN port.
2-40
Page 71
CLI commands
Config context
bridge priority
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
bridge priority <number>
Sets the bridge priority for the spanning tree.
The spanning tree uses the bridge ID to elect the root bridge and the designated bridges. The
bridge ID is built with the MAC address of the bridge and the bridge priority. The first 2 most
significant bytes are the bridge priority and the next 6 bytes are the MAC address. To control
which bridge will become the root bridge, you can configure the bridge priority parameter on the
bridges. The root will be the bridge with the lowest bridge ID. The Bridge priority has a valid range
of 0 to 0xFFFF. The default value is the middle value: 0x8000.
bridge protocol ieee
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
bridge protocol ieee
Enable the bridge spanning tree protocol to prevent undesirable loops from occurring in the
network that may result in decreased throughput.
no bridge protocol ieee
Disable the bridge spanning tree protocol.
bridge protocol ieee vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
bridge protocol ieee vlan
Enable the bridge spanning tree protocol for VLANs.
no bridge protocol ieee vlan
Disable the bridge spanning tree protocol for VLANs.
ip route gateway
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip route gateway<destination>/<mask> <gateway> <[metric]>
Adds a static route.
no ip route gateway <destination>/<mask> <gateway> <[metric]>
Removes the specified static route.
Parameters
<destination> Traffic addressed to this IP address will be routed.
<mask> Indicates the number of bits in the destination address that is checked for a
match.
<gateway> Indicates the IP address of the gateway the AP will forward routed traffic
to. The gateway address must be on the same subnet as one of the
available interfaces (Internet port or LAN port).
<metrix> Indicates the priority of a route. If two routes exist for a destination
address then the AP chooses the one with the lower metric.
2-41
Page 72
CLI commands
Config context
dot1x reauth
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot1x reauth
Enable this option to force 802.1X client stations to reauthenticate.
no dot1x reauth
Disables 802.1X reauthentication.
dot1x reauth period
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot1x reauth period (15m | 30m | 1h | 2h | 4h | 8h | 12h)
Sets the 802.1X reauthentication interval. Client stations must reauthenticate when this interval
expires.
dot1x reauth terminate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot1x reauth terminate
Enable this option to allow client stations to remain connected during re-authentication. Client
traffic is blocked only when re-authentication fails.
no dot1x reauth terminate
Disabled this option to block client traffic during re-authentication and only activate traffic again
if authentication succeeds.
dot1x supplicant timeout
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot1x supplicant timeout <number>
Sets the 802.1X supplicant time-out.
Parameters
<seconds> time-out in seconds.
dynamic key
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dynamic key
Enables dynamic key support for 802.1X and WPA.
no dynamic key
Disables dynamic key support for 802.1X and WPA.
2-42
Page 73
CLI commands
Config context
dynamic key interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dynamic key interval (5m | 10m | 15m | 30m | 1h | 2h | 4h | 8h | 12h)
Specifies how often (in minutes or hours) that the group (broadcast) key is changed for 802.1X
and WPA.
add wireless ip-qos profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
add wireless ip-qos profile <name>
Adds the specified profile to the list of IP QoS profiles in effect for all local mesh links.
<profile-name> Name of an existing IP QoS profile.
delete wireless ip-qos profile all
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete wireless ip-qos profile all
Clears the list of IP QoS profiles currently in effect for all local mesh links.
delete wireless ip-qos profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete wireless ip-qos profile <name>
Removes the specified profile from the list of IP QoS profiles in effect for all local mesh links.
<profile-name> Name of an existing IP QoS profile currently in the profile list for all local
mesh links.
wireless link qos
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless link qos (disabled | 802.1p | wme | very-high | high | normal | low |
tos | diffsrv)
Sets the local mesh QoS policy.
sensor discovery mode
Supported on: MSM320 MSM335
sensor discovery mode (id | ip)
Sets the method the AP will use to communicate with the RF Manager Server.
Parameters
id Connect using the Server ID of the RF Manager Server.
ip Connect using the IP address or hostname of the RF Manager Server.
Description
For these methods to work, the following must be true:
2-43
Page 74
CLI commands
Config context
The AP must be able to reach the RF Manager Server via a network connected to port 1 or
port 2. For example, you should be able to ping the RF Manager Server’s IP address from the
AP.
If there are any firewalls between the AP and the RF Manager Server, then TCP and UDP ports
3851 must be open bi-directionally.
If using the hostname option, an entry must be created on the network DNS server that points
to the IP address of the RF Manager Server.
If using the Server ID option, support for multicast traffic must be enabled on all routers and
switches connected between the AP and the RF Manager Server.
sensor network detector
Supported on: MSM320 MSM335
sensor network detector
Enable the Network Detector.
no sensor network detector
Disable the Network Detector.
sensor server id
Supported on: MSM320 MSM335
sensor server id <id>
Sets the server ID of the RF Manager Server to connect to.
Parameters
ID Specify the Server ID of the RF Manager Server to connect to. Set the
Server ID to 0 to have the AP send a discovery request to all active HP RF
Manager Servers. The AP will connect to the first server that responds to
the discovery request.
sensor server name
Supported on: MSM320 MSM335
sensor server name <name>
Sets the IP address or hostname of the RF Manager Server to connect to.
Parameters
Name Specify the IP address of the RF Manager Server or its hostname. If a
hostname is specified, the AP must be able to resolve it via DNS—that is,
an entry must be created on the network DNS server that points to the IP
address of the RF Manager Server.
config-version
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
config-version <string>
Sets a string to identify the user configuration version.
2-44
Page 75
New sflow
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
sflow
Enables sFlow.
no sflow
Disables sFlow.
New show sflow agent
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show sflow agent
Displays read-only sFlow agent information.
New show sflow controller stats
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show sflow controller stats
CLI commands
Config context
Displays read-only sFlow controller statistics.
New show sflow device stats
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show sflow device stats <macaddress>
Displays read-only sFlow device statistics.
New sflow destination
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
sflow <receiver> destination <ipaddress> [<port>] [<80211toethernet>]
Sets the IP address of an sFlow collector/management station.
New show sflow destination
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show sflow <receiver> destination
Shows sFlow receiver configuration.
New show sflow sampling-polling
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show sflow <receiver> sampling-polling [<interface>]
Shows sFlow sampling and polling configuration for a receiver.
2-45
Page 76
CLI commands
Config context
New sflow sampling
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
sflow <receiver> sampling <interface> <rate>
Specifies the number of packets between samples. For example, if set to 5, approximately every
fifth packet will be sampled (There is some jitter introduced purposefully into the sample
collection). A value of 0 disables sampling.
New sflow polling
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
sflow <receiver> polling <interface> <interval>
Specifies the maximum interval (seconds) between polling of counters. 0 disables polling.
New mac lockout entry
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac lockout entry <mac>
Adds a new entry to the MAC lockout list.
no mac lockout entry <mac>
Removes the entry from the MAC lockout list.
New show mac lockout
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
show mac lockout
Displays all entries in the MAC lockout list.
New supplicant 802dot1x
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
supplicant 802dot1x
Enables the 802.1X supplicant.
no supplicant 802dot1x
Disables 802.1X supplicant.
New supplicant anonymous identity
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
supplicant anonymous identity <identitiy>
Sets the 802.1X supplicant anonymous identity.
New supplicant eap
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
supplicant eap (peap0 | peap1 | ttls) <user> <password>
Changes the EAP configuration.
2-46
Page 77
CLI commands
Port 2 port interface context
Port 2 port interface context
Path: View > Enable > Config > Port 2 port interface
Use this context to configure the Port 2 port.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
duplex
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
duplex (auto | half | full)
Sets the duplex mode on Port 2.
Parameters
auto Lets the AP automatically set duplex mode based on the type of equipment
it is connected to.
half Forces the port to operate in half duplex mode.
full Forces the port to operate in full duplex mode.
speed
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
speed (auto | 10 | 100)
Sets the speed of the Port 2 port.
Parameters
auto Lets the AP automatically set port speed based on the type of equipment it
is connected to.
100 Forces the port to operate at 100 mbps.
10 Forces the port to operate at 10 mbps.
vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan <id>
Sets the default VLAN ID. Range: 1 - 4094. All outgoing traffic that does not have a VLAN already
assigned to it, is sent on this VLAN.
no vlan
Deletes the default VLAN ID.
2-47
Page 78
CLI commands
Port 2 port interface context
vlan compatibility mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan compatibility mode
When this option is enabled, the AP sends all management traffic AND all untagged traffic on both
the default VLAN and untagged.
no vlan compatibility mode
Disables VLAN and untagged compatibility mode.
vlan-management filter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan-management filter
Restricts the default VLAN to carry management traffic only.
no vlan-management filter
Does not restrict the default VLAN to carry management traffic only.
Management traffic includes:
all traffic that is exchanged by the AP and the access controller
all communications with RADIUS servers
HTTPS sessions to the management tool
SNMP traffic
interface vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface vlan <networkname>
Switches to the specified VLAN interface or create a new VLAN interface with the specified VLAN
definition.
no interface vlan <networkname>
Deletes the specified VLAN.
2-48
Page 79
CLI commands
Port 1 port interface context
Port 1 port interface context
Path: View > Enable > Config > Port 1 port interface
Use this context to configure the Port 1 port.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
duplex
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
duplex (auto | half | full)
Sets the duplex mode on Port 1.
Parameters
auto Lets the AP automatically set duplex mode based on the type of equipment
it is connected to.
half Forces the port to operate in half duplex mode.
full Forces the port to operate in full duplex mode.
speed
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
speed (auto | 10 | 100)
Sets the speed of the Port 1 port.
Parameters
auto Lets the AP automatically set port speed based on the type of equipment it
is connected to.
100 Forces the port to operate at 100 mbps.
10 Forces the port to operate at 10 mbps.
vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan <id>
Sets the default VLAN ID. Range: 1 - 4094. All outgoing traffic that does not have a VLAN already
assigned to it, is sent on this VLAN.
no vlan
Deletes the default VLAN ID.
2-49
Page 80
CLI commands
Port 1 port interface context
vlan compatibility mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan compatibility mode
When this option is enabled, the AP sends all management traffic AND all untagged traffic on both
the default VLAN and untagged.
no vlan compatibility mode
Disable VLAN and untagged compatibility mode.
vlan-management filter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan-management filter
Restricts the default VLAN to carry management traffic only.
no vlan-management filter
Does not restrict the default VLAN to carry management traffic only.
Management traffic includes:
all traffic that is exchanged by the AP and the access controller
all communications with RADIUS servers
HTTPS sessions to the management tool
SNMP traffic
interface vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
interface vlan <id>[-<id2>]
Switches to the specified VLAN interface or create a new VLAN interface with the specified ID.
no interface vlan <id>[-<id2>]
Deletes the specified VLAN interface.
Parameters
<id> VLAN ID. Range: 1 - 4094.
<id2> VLAN ID. When specified, is the last value in a range.
2-50
Page 81
CLI commands
WAN IP interface context
WAN IP interface context
Path: View > Enable > Config > WAN IP interface
Use this context to configure various IP-networking related settings on the Internet port.
pppoe client user
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
pppoe client user <username> <password>
Sets the PPPoE username and password.
no pppoe client user
Deletes the PPPoE username.
Parameters
<username> The username assigned to you by your ISP. The AP will use this username
to log on to your ISP when establishing a PPPoE connection.
<password> The password assigned to you by your ISP. The AP will use this username
to log on to your ISP when establishing a PPPoE connection.
ip address mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip address mode (dhcp | pppoe | static)
Sets the IP addressing mode for Port 2.
Parameters
dhcp Dynamic host configuration protocol. The DHCP server will automatically
assign an address to the AP, which functions as a DHCP client.
pppoe Point-to-point protocol over Ethernet. The PPPoE server will automatically
assign an IP address to the AP. You need to supply a username and
password so the AP can log on.
static This option enables you to manually assign an IP address to the AP.
ip address
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip address <ip address>/<mask>
Sets a static IP address for the port.
Parameters
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
ip default-gateway
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip default-gateway <ip address>
Sets the IP address of the default gateway.
2-51
Page 82
CLI commands
WAN IP interface context
no ip default-gateway
Deletes the default gateway IP address.
Parameters
<address> IP address.
ip address dhcp client-id
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip address dhcp client-id <id>
Specifies an ID to identify the AP to a DHCP server. This parameter is not required by all ISPs.
no ip address dhcp client-id
Deletes the specified DHCP client id.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
pppoe auto-reconnect
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
pppoe auto-reconnect
The AP will automatically attempt to reconnect if the connection is lost.
no pppoe auto-reconnect
The AP will not automatically attempt to reconnect if the connection is lost.
pppoe mru
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
pppoe mru <bytes>
Specifies the maximum receive unit.
Changes to this parameter should only be made according to the recommendations of your ISP.
Incorrectly setting this parameter can reduce the throughput of your Internet connection.
Parameters
<bytes> Maximum size (in bytes) of a PPPoE packet when receiving. Range: 500 -
1500 bytes.
pppoe mtu
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
pppoe mtu <bytes>
Specifies the maximum transmit unit.
Changes to this parameter should only be made according to the recommendations of your ISP.
Incorrectly setting this parameter can reduce the throughput of your Internet connection.
2-52
Page 83
CLI commands
WAN IP interface context
Parameters
<bytes> Maximum size (in bytes) of a PPPoE packet when transmitting. Range: 500
- 1500 bytes.
pppoe unnumbered
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
pppoe unnumbered
Enable unnumbered mode.
no pppoe unnumbered
Disable unnumbered mode.
This feature is useful when the AP is connected to the Internet and NAT is not being used. Instead
of assigning two IP addresses to the AP, one to the Internet port and one to the LAN port, both
ports can share a single IP address. This is especially useful when a limited number of IP
addresses are available to you.
2-53
Page 84
CLI commands
Wireless context
Wireless context
Path: View > Enable > Config > Wireless
Use this context to configure wireless settings.
end
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
end
Switches to parent context.
radio active
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
radio active
Enables the radio.
no radio active
Disables the radio.
rts threshold
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
rts threshold <value>
Sets the RTS threshold.
no rts threshold
Deletes the RTS threshold value.
Parameters
< value> Threshold value in the range 128 and 1540.
Description
Use this parameter to control collisions on the link that can reduce throughput. If the Status >
Wireless page on the management tool shows increasing values for Tx multiple retry frames or Tx
single retry frames, you should adjust this value until the errors clear up. Start with a value of 1024
and then decrease to 512 until errors are reduced or eliminated.
Using a small value for RTS threshold can affect throughput.
If a packet is larger than the threshold, the AP will hold it and issue a request to send (RTS)
message to the client station. Only when the client station replies with a clear to send (CTS)
message will the AP send the packet. Packets smaller than the threshold are transmitted without
this handshake.
distance
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
distance (small | medium | large)
Sets the distance between access points.
2-54
Page 85
CLI commands
Wireless context
Use this parameter to adjust the receiver sensitivity of the AP. This parameter should only be
changed if:
you have more than one wireless access point installed in your location
you are experiencing throughput problems
In all other cases, use the default setting of Large.
If you have installed multiple APs, reducing the receiver sensitivity of the AP from its maximum
will help to reduce the amount of crosstalk between the wireless stations to better support
roaming clients. By reducing the receiver sensitivity, client stations will be more likely to connect
with the nearest access point.
dot11
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 <mode> <frequency>
Sets the wireless mode and the frequency the AP will operate at.
Parameters
<mode> Sets the transmission speed and frequency band. The available options are
determined by the wireless card installed in the AP, and may include:
a: Selects 802.11a providing 54 Mbps in the 5 GHz frequency band.
b: Selects 802.11b providing 11 Mbps in the 2.4 GHz frequency band.
g: Selects 802.11g providing 54 Mbps in the 2.4 GHz frequency band.
bg: Selects 802.11b + 802.11g providing 11 and 54 Mbps in the 2.4 GHz
frequency band.
n: Selects 802.11n.
an: Selects 802.11n + 802.11a, on the 5Ghz frequency band.
gn: Selects 802.11n + 802.11g, on the 2.4Ghz frequency band.
bgn: Selects 802.11n + 802.11g + 802.11b, on the 2.4Ghz frequency band.
<frequency> Sets the operating frequency by specifying a number in GHz or by
specifying a channel number. The frequencies that are available are
determined by the radio installed in the AP and the regulations that apply
in your country.
For optimum performance when operating in 802.11b or 802.11g modes,
choose a frequency that differs from other wireless access points operating
in neighboring cells by at least 25 MHz.
If operating in 802.11a mode, all channels are non-overlapping.
transmit power
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
transmit power (DB | max)
Sets the maximum transmission power of the wireless radio.
Parameters
<db> Power is specified in steps of 1dBm. The maximum setting is 18 dBm.
Note: The actual transmit power used may less than the value specified. The AP determines the
power to used based on the settings you made for regulatory domain, wireless mode, and
operating frequency.
2-55
Page 86
CLI commands
Wireless context
antenna bidirectionnal
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
antenna bidirectionnal (diversity | main | auxiliary)
Sets the antenna to transmit and receive on. Select diversity to transmit and receive on both
antennas.
Parameters
diversity In this mode both antennas are used to transmit and receive. The AP
supports both transmit and receive diversity.
main Transmit and receive on the main antenna only.
aux Transmit and receive on the aux antenna only.
antenna gain
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
antenna gain <number>
Used only for Radar detection, records gain (in 5GHz band) of external antenna installed on
device. Does not affect output power.
autochannel skip
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
autochannel skip <chan>
Adds the specified channel to the list of channels that are not allowed to be selected by the Auto
Channel algorithm.
no autochannel skip <chan>
Removes the specified channel to the list of channels that are not allowed to be selected by the
Auto Channel algorithm.
beacon interval
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
beacon interval <value>
Sets the beacon interval.
Parameters
< value> Beacon interval value in the range 20 and 500 time units (TU) (1 TU =
1024us).
dot11 automatic frequency
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 automatic frequency
Enable this option to have the AP automatically determine the best operating frequency.
no dot11 automatic frequency
Disable automatic frequency selection.
2-56
Page 87
CLI commands
Wireless context
dot11 automatic frequency period
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 automatic frequency period (disabled | 1h | 2h | 4h | 8h | 12h | 24h)
Specify how often the frequency setting is re-evaluated when automatic frequency selection is
enabled.
dot11 automatic frequency time
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 automatic frequency time <time>
Specify when the channel should be re-evaluated.
dot11 automatic transmit-power
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 automatic transmit-power
Enables automatic transmit power selection.
no dot11 automatic transmit-power
Disables automatic transmit power selection.
dot11 automatic transmit-power period
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 automatic transmit-power period (1h | 2h | 4h | 8h | 12h | 24h)
Sets the interval at which the transmit power setting is re-evaluated when automatic power
selection is enabled.
New maximum clients
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
maximum clients <value>
Sets the maximum number of wireless client stations that can be associated at the same time on
this radio.
Parameters
< value> Maximum clients value in the range 1 and 255.
multicast rate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
multicast rate (1 | 2 | 5.5 | 6 | 9 | 11 | 12 | 18 | 24 | 36 | 48 | 54)
Sets the transmit rate for multicast traffic.
This is a fixed rate, which means that if a station is too far away to receive traffic at this rate, then
the multicast will not be seen by the station. By rasing the multicast rate you can increase overall
throughput significantly.
2-57
Page 88
CLI commands
Wireless context
station distance
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
station distance (0km | 5km | 10km | 15km | 20km | 25km | 30km | 35km)
Fine tunes internal timeout settings to account for the distance that wireless links span. For
normal operation, the AP is optimized for links of less than 1 km.
This is a global setting that is useful when creating wireless links to remote sites. However, it also
applies to all wireless connection made with the radio, not just for wireless links. Therefore, if you
are also using the radio to serve local wireless client stations, adjusting this setting may lower the
performance for clients with marginal signal strength or when interference is present.
(Essentially, it means that if a frame needs to be retransmitted it will take longer before the actual
retransmit takes place.)
dot11 mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot11 mode (monitor | ap+wds | ap-only | wds-only | sensor)
Sets the operating mode for the radio.
spectralink view
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
spectralink view
Enables the use of spectralink view.
no spectralink view
Disables the use of spectralink view.
New dot11n channel extension
Supported on: MSM422 MSM410
dot11n channel extension (above | below)
Selects the 802.11n channel extension. Applicable only in the 2.4 GHz band and a 40 MHz channel
width.
dot11n channel width
Supported on: MSM422 MSM410
dot11n channel width (40 | 20 | auto)
Select the 802.11n channel width.
New dot11n guard interval
Supported on: MSM422 MSM410
dot11n guard interval (short | long)
Selects the 802.11n guard interval.
2-58
Page 89
dot11n mimo
Supported on: MSM422 MSM410
dot11n mimo (3x3 | 2x2 | 2x3)
Sets the MIMO mode for 802.11n.
New dot11n multicast rate
Supported on: MSM422 MSM410
dot11n multicast rate <rate>
Sets the multicast rate for use with 802.11n networks.
bandwidth
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
bandwidth
Enables bandwidth control.
no bandwidth
CLI commands
Wireless context
Disables bandwidth control.
bandwidth max
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
bandwidth max <rate>
Sets the maximum data rate on the wireless port in kbps.
Parameters
<rate> Maximum data rate. Range: 50 - 500000 kbps.
2-59
Page 90
CLI commands
Virtual AP context
Virtual AP context
Path: View > Enable > Config > Virtual AP
Use this context to configure VSC profiles (formerly called VAPs).
By default, one VSC profile exists with the name "HP". This is the default profile and cannot be
deleted.
virtual ap name
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
virtual ap name <name>
Change the VAP (VSC) name.
ingress interface
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ingress interface (wireless | wireless) <name>
Sets the specified interface as the ingress interface traffic will be accepted on.
no ingress interface (wireless | wireless) <name>
Removes the specified interface as an ingress interface.
guest-mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
guest-mode
Enables broadcast of the wireless network name (SSID).
no guest-mode
Disables broadcast of the wireless network name (SSID).
max-association
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
max-association <stations>
Sets the maximum number of clients stations that can associate with this VAP (VSC).
<stations> Number of client stations. Range: 1 - 255.
ssid name
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ssid name <name>
Specifies the WLAN name (SSID) for the profile.
2-60
Page 91
vlan
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
vlan <id>
Assigns a VLAN ID to this VAP (VSC).
no vlan
Deletes the VLAN ID for this VAP (VSC).
Parameters
<id> VLAN ID. Range: 1 - 4094.
encryption key 1
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
encryption key <key> <value>
Sets WEP key 1.
no encryption key <key>
Deletes WEP key 1.
CLI commands
Virtual AP context
Parameters
<key> WEP key number. Range: 1 - 4. Keys 2 to 4 are only supported on the first
WLAN profile.
<value> Key value. The number of characters you specify for a key determines the
level of encryption the AP will provide.
For 40-bit encryption, specify 5 ASCII characters or 10 HEX digits.
For 128-bit encryption, specify 13 ASCII characters or 26 HEX digits.
encryption key format
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
encryption key format (hex | ascii)
Specify the WEP key format.
Parameters
hex Hex keys should only include the following digits: 0-9, a-f, A-F
ascii ASCII keys are much weaker than carefully chosen hex keys. You can
include ASCII characters between 32 and 126, inclusive, in the key.
However, note that not all client stations support non-alphanumeric
characters such as spaces, punctuation, or special symbols in the key.
transmit key
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
transmit key <key number>
Sets the key the AP will use to encrypt transmitted data. All four keys are used to decrypt received
data.
Parameters
<key number> Transmit key number. Range: 1 -4.
2-61
Page 92
CLI commands
Virtual AP context
authentication server access controller
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server access controller
Use the access controller to authenticate 802.1X or WPA logins.
authentication server accounting
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server accounting
Enables RADIUS accounting for this VSC (VAP).
no authentication server accounting
Disables RADIUS accounting for this VSC (VAP).
authentication server accounting radius profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server accounting radius profile <name>
Sets RADIUS accounting to use the specified RADIUS profile.
no authentication server accounting radius profile
Removes accounting support for 802.1X.
authentication server radius
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server radius <name>
Sets the RADIUS profile to use for 802.1X or WPA authentication.
dot1x authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
dot1x authentication (local | radius | active-directory)
Sets the authentication for 802.1X and WPA.
wpa-psk
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wpa-psk <key>
Sets the WPA preshared key.
no wpa-psk
Deletes the WPA preshared key.
Parameters
password Specify a key that is between 8 and 64 ASCII characters in length. It is
2-62
recommended that the preshared key be at least 20 characters long, and be
a mix of letters and numbers.
Page 93
CLI commands
Virtual AP context
Description
The AP uses the key you specify to generate the TKIP keys that encrypt the wireless data stream.
Since this is a static key, it is not as secure as using dynamically generated keys.
authentication server accounting radius stationid case
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server accounting radius stationid case (uppercase | lowercase)
Specifies the case applied to the station delimiter if it is a letter.
authentication server accounting radius stationid delimiter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
authentication server accounting radius stationid delimiter (null | colon |
dash | dot | space | comma | under)
Specifies the one-character delimiter that will be used to format both the calling station ID and the
called station ID attributes in RADIUS packets.
wireless filters
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless filters
Enables the wireless security filters which only allow traffic to flow between the AP and a specific
upstream device (such as a HP service controller).
no wireless filters
Do not limit traffic flow between the AP and an upstream device.
This prevents wireless users from accessing resources on the backbone LAN that interconnects
the AP and the upstream device.
wireless filters mac
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless filters mac <mac>
Sets the MAC address of the upstream device to send traffic to.
no wireless filters mac <mac>
Deletes the MAC address of the upstream device to send traffic to.
wireless filters rule input
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless filters rule input <rule>
Adds a custom filter definition for incoming wireless traffic.
Use this command to define custom security filters for incoming wireless traffic. Filters are
specified using standard pcap syntax (http://www.tcpdump.org/tcpdump_man.html) with the
addition of a few HP-specific placeholders. These placeholders can be used to refer to specific
MAC addresses and are expanded by the AP when the filter is activated. Once expanded, the filter
must respect the pcap syntax. The pcap syntax is documented in the tcpdump man page:
2-63
Page 94
CLI commands
Virtual AP context
Placeholders
%a - MAC address of the access controller.
%b - MAC address of the bridge.
%g - Mac address of the default gateway assigned to the AP.
%w - MAC address of wireless port.
wireless filters rule output
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless filters rule output <rule>
Adds a custom filter definition for outgoing wireless traffic.
Use this command to define custom security filters for outgoing wireless traffic. Filters are
specified using standard pcap syntax (http://www.tcpdump.org/tcpdump_man.html) with the
addition of a few HP-specific placeholders. These placeholders can be used to refer to specific
MAC addresses and are expanded by the AP when the filter is activated. Once expanded, the filter
must respect the pcap syntax. The pcap syntax is documented in the tcpdump man page:
Placeholders
%a - MAC address of the access controller.
%b - MAC address of the bridge.
%g - Mac address of the default gateway assigned to the AP.
%w - MAC address of wireless port.
wireless filters type
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wireless filters type (mac | gateway | rules)
Sets the type of wireless security filter to use.
Parameters
mac Traffic is forwarded to an upstream device with a specific MAC address.
Wireless security filters use the default definitions.
gateway Traffic is forwarded to the default gateway assigned to the AP. Wireless
security filters use the default definitions.
custom Lets you define custom security filters and address for the upstream
device.
Description
The AP features an intelligent bridge which can apply security filters to safeguard the flow of
wireless traffic. The filters limit both incoming and outgoing traffic as defined below, and force
the AP to exchange traffic with a specific upstream device. If the AP is configured to use the
services of a HP access controller, then the default security filters are automatically enabled and
all traffic is sent to the access controller.
Default filters for incoming wireless traffic
Applies to traffic sent from wireless client stations to the AP.
Accepted
Any IP traffic addressed to the access controller.
2-64
Page 95
CLI commands
Virtual AP context
PPPoE traffic (The PPPoe server must be the upstream device.)
IP broadcast packets, except NetBIOS
Certain address management protocols (ARP, DHCP) regardless of their source address.
Any traffic addressed to the AP, including 802.1X.
Blocked
All other traffic is blocked. This includes NetBIOS traffic regardless of its source/destination
address. TTPS traffic not addressed to the AP (or upstream device) is also blocked, which
means wireless client stations cannot access the management tool on other HP products.
Default filters for outgoing wireless traffic
Applies to traffic sent from the AP to wireless client stations.
Accepted
Any IP traffic coming from the upstream device, except NetBIOS packets.
PPPoE traffic from the upstream device.
IP broadcast packets, except NetBIOS
ARP and DHCP Offer and ACK packets.
Any traffic coming from the AP itself, including 802.1X.
Blocked
All other traffic is blocked. This includes NetBIOS traffic regardless of its source/destination
address.
mac-filters local
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac-filters local
Enables the MAC filter list.
no mac-filters local
Disables the MAC filter list.
mac-filters
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac-filters <address>
Adds an address to the MAC filter list.
no mac-filters <address>
Remove the specified address from the MAC filter list.
Parameters
<address> MAC address. Specify 6 pairs of hexadecimal numbers separated by
colons, with the values a to f in lowercase. For example: 00:00:00:0a:0f:01
2-65
Page 96
CLI commands
Virtual AP context
Description
This feature enables you to control access to the AP based on the MAC address of client stations.
You can either block access or allow access, depending on your requirements. When both this
option and the MAC-based authentication options are enabled, the following applies: if a user’s
MAC address does not appear in the MAC filtering list, then MAC-based authentication takes place
for that user.
mac-filters mode
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac-filters mode (allow | block)
Either allow or block access to the wireless network for client stations whose addresses appear in
the MAC filter list.
mac authentication accounting
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication accounting
Enables RADIUS accounting for this VAP (VSC).
no mac authentication accounting
Disables RADIUS accounting for this VAP (VSC).
mac authentication accounting radius profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication accounting radius profile <name>
Sets RADIUS accounting to use the specified RADIUS profile.
no mac authentication accounting radius profile
Disables accounting support for MAC authentication.
mac authentication radius profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication radius profile <radiusname>
Specifies the name of the RADIUS profile to use for MAC-based authentication.
no mac authentication radius profile
Do not use a RADIUS profile.
mac authentication radius stationid case
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication radius stationid case (uppercase | lowercase)
Specifies the case applied to the station delimiter if it is a letter.
2-66
Page 97
CLI commands
Virtual AP context
mac authentication radius stationid delimiter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication radius stationid delimiter (null | colon | dash | dot | space
| comma | under)
Specifies the one-character delimiter that will be used to format both the calling station ID and the
called station ID attributes in RADIUS packets.
mac authentication
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
mac authentication
Enables support for MAC-based authentication.
no mac authentication
Disable support for MAC-based authentication.
add ip filter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
add ip filter <ip address>/<mask>
Adds an IP filter to the list of destination addresses that traffic will be accepted for. All other
traffic will be blocked.
If the list is empty, then all wireless-to-wired LAN traffic is permitted.
Where:
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
delete ip filter
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete ip filter <ip address>/<mask>
Deletes the specified address from the IP filter list.
If the list is empty, then all wireless-to-wired LAN traffic is permitted.
Where:
<address> IP address.
</mask> Subnet mask in CIDR format. Specifies the number of bits in the mask.
delete ip filter all
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete ip filter all
Deletes all addresses from the IP filter list.
2-67
Page 98
CLI commands
Virtual AP context
ip filters
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
ip filters
Activates the IP filter which enables you to block wireless-to-wired LAN traffic on this profile
based on its destination address.
no ip filters
Disables the IP filter for this profile.
active
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
active
Enable this VAP (VSC).
no active
Disable this VAP (VSC).
beacon dtim count
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
beacon dtim count <number>
Defines the DTIM period in the beacon.
Client stations use the DTIM to wake up from low-power mode to receive multicast traffic. The AP
transmits a beacon every 100 ms. The DTIM counts down with each beacon that is sent, therefore
if the DTIM is set to 5, then client stations in low-power mode will wake up every 500 ms (.5
second) to receive multicast traffic.
beacon transmit power
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
beacon transmit power
Advertise the current transmit power setting in the beacon.
no beacon transmit power
Do not advertise the current transmit power setting in the beacon.
New data rate
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
data rate (a | b | g | bg | n) <rate>
Enable the given data rate for a particular PHY type.
no data rate (a | b | g | bg | n) <rate>
Disable the given data rate for a particular PHY type.
2-68
Page 99
CLI commands
Virtual AP context
add ip-qos profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
add ip-qos profile <name>
Adds the specified profile to the list of IP QoS profiles in effect for this VSC (VAP).
<profile-name> Name of an existing IP QoS profile.
delete ip-qos profile all
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete ip-qos profile all
Clears the list of IP QoS profiles currently in effect for this VSC (VAP).
delete ip-qos profile
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
delete ip-qos profile <name>
Removes the specified profile from the list of IP QoS profiles in effect for this VSC (VAP).
<profile-name> Name of an existing IP QoS profile currently in the profile list for this VSC
(VAP).
qos
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
qos ( 802.1p | very-high | high | normal | low | diffsrv | tos | default | vap0
| vap1 | vap2 | vap3)
Sets the QoS level for this profile.
no qos
Disables QoS for this profile.
Four traffic queues are provided based on the WME standard. In order of priority, these queues
are:
1: Voice traffic
2: Video traffic
3: Best effort data traffic
4: Background data traffic
Each QoS priority mechanism maps traffic to one of the four traffic queues. Client stations that do
not support the QoS mechanism for the profile they are connected to are always assigned to queue
3.
Important: Traffic delivery is based on strict priority (per the WME standard). Therefore, if
excessive traffic is present on queues 1 or 2, it will reduce the flow of traffic on queues 3 and 4.
2-69
Page 100
CLI commands
Virtual AP context
802.1p Traffic from 802.1p client stations is classified based on the VLAN priority
field present within the VLAN header. When this mechanism is selected,
the AP will advertise WME capabilities, enabling WME clients to associate
and take advantage of them. This setting has no effect on legacy clients.
Note: To support 802.1p, the wireless profile must have a VLAN assigned to
it, which means that client station traffic is forwarded onto the LAN port
only.
vap0 to vap3 Allows a specific priority level to be specified for all traffic on a VAP (VSC)
profile. This enables client stations without a QoS mechanism to set traffic
priority by connecting to the appropriate SSID.
If you enable this priority mechanism, it takes precedence regardless of the
priority mechanism supported by associated client stations. For example,
if you set SSID-based low priority for a profile, all devices that connect to
the profile have their traffic set at this priority
Mapping to the traffic queues is as follows: vap0 or very-high=queue 1,
vap1 or high=queue 2, vap2 or normal=queue 3, vap3 or low=queue 4
diffsrv Differential services is a method for defining IP traffic priority on a per-hop
basis. The Differential Service bits are defined in RFC2474 and are
composed of the six most significant bits of the IP TOS field. These bits
define the class selector code points which the CN320 maps to the
appropriate traffic queue. (default setting)
tos The IP TOS (type of service) field can be used to mark prioritization or
special handling for IP packets.
upstream diffserv tagging
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
upstream diffserv tagging
Enables upstream diffserv tagging.
no upstream diffserv tagging
Disables upstream diffserv tagging.
wmm advertising
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
wmm advertising
Enables WMM information element advertising.
no wmm advertising
Disables WMM information element advertising.
location-aware group
Supported on: MSM422 MSM320 MSM410 MSM310 MSM335
location-aware group <name>
Sets the specified group name for the access point.
no location-aware group
Deletes the specified group name for the access point.
2-70
 Loading...