

Page 1
A l l R i g h t s R e s e r v e d 1 9 9 7 - 2 0 0 8
E
N A B L E
-I T
- P r o p r i e t a r y a n d C o n f i d e n t i a l
Enable-IT 8424
802 . 1 1g / 802. 1 1b / WPA
Wir e less A cce s s Po i n t
User Manual
Page 2
P a g e 2 o f
9 3
Copyright © 1997- 2008, Enable-IT, Inc. All rights reserved. No part of this documentation
may be reproduced in any form or by any means or used to make any derivative work (such
as translation, transformation, or adaptation) without written permission from Enable-IT, Inc.
Enable-IT, Inc reserves the right to revise this documentation and to make changes in
content from time to time without obligation on the part of Enable-IT, Inc to provide
notification of such revision or change.
Enable-IT, Inc provides this documentation without warranty, term, or condition of any kind,
either implied or expressed, including, but not limited to, the implied warranties, terms or
conditions of merchantability, satisfactory quality, and fitness for a particular purpose.
Enable-IT, Inc may make improvements or changes in the product(s) and/or the
program(s) described in this documentation at any time.
If there is any software on removable media described in this documentation, it is furnished
under a license agreement included with the product as a separate document, in the hard
copy documentation. If you are unable to locate a copy, please contact Enable-IT, Inc and a
copy will be provided to you.
UNITED STATES GOVERNMENT LEGEND
If you are a United States government agency, then this documentation and the software
described herein are provided to you subject to the following:
All technical data and computer software are commercial in nature and developed solely at
private expense. Software is delivered as "Commercial Computer Software" as defined in
DFARS 252.227-7014 (June 1995) or as a "commercial item" as defined in FAR 2.101 (a)
and as such is provided with only such rights as are provided in Enable-IT, Inc's standard
commercial license for the Software.
Technical data is provided with limited rights only as provided in DFAR 252.227-7015 (Nov
1995) or FAR 52.227-14 (June 1987), whichever is applicable. You agree not to remove or
deface any portion of any legend provided on any licensed program or documentation
contained in, or delivered to you in conjunction with, this User Guide.
Unless otherwise indicated, Enable-IT, Inc registered trademarks are registered in the
United States and may or may not be registered in other countries
Page 3
P a g e 3 o f
9 3
T
ABLE OF CONTENTS
CHAPTER 1 INTRODUCTION .................................................................................................................................. 4
Features of your Wireless Access Point ........................................................................................................ 4
Package Contents ............................................................................................................................................. 6
Physical Details ................................................................................................................................................. 6
CHAPTER 3 ACCESS POINT SETUP ...................................................................................................................... 8
Ov e rvi ew ............................................................................................................................................................ 8
Setup using the Windows Utility ..................................................................................................................... 8
Access Control ................................................................................................................................................ 12
Security Profiles .............................................................................................................................................. 14
Security Profile Screen ................................................................................................................................... 15
System Screen ................................................................................................................................................ 25
Wireless Screens ............................................................................................................................................ 26
Basic Settings Screen .................................................................................................................................... 26
Advanced Settings .......................................................................................................................................... 29
CHAPTER 4 PC AND SERVER CONFIGURATION .............................................................................................. 31
Ov e rvi ew .......................................................................................................................................................... 31
Using WEP ....................................................................................................................................................... 31
Using WPA-802.1x .......................................................................................................................................... 32
802.1x Server Setup (Windows 2000 Server) ............................................................................................... 33
802.1x Client Setup on Windows XP ............................................................................................................. 43
Using 802.1x Mode (without WPA) ................................................................................................................ 51
Using WPA-PSK .............................................................................................................................................. 52
Using WPA-802.1x .......................................................................................................................................... 53
802.1x Server Setup (Windows 2000 Server) ............................................................................................... 54
802.1x Client Setup on Windows XP ............................................................................................................. 64
Using 802.1x Mode (without WPA) ................................................................................................................ 72
CHAPTER 5 OPERATION AND STATUS .............................................................................................................. 72
Operation ......................................................................................................................................................... 72
Status Screen .................................................................................................................................................. 72
CHAPTER 6 ACCESS POINT MANAGEMENT ..................................................................................................... 78
Ov e rvi ew .......................................................................................................................................................... 78
Admin Login Screen ....................................................................................................................................... 78
Auto Config/Update ........................................................................................................................................ 80
Config File........................................................................................................................................................ 82
Log Settings (Syslog) ..................................................................................................................................... 83
Rogue APs ....................................................................................................................................................... 84
SNMP ................................................................................................................................................................ 85
Upgrade Firmware .......................................................................................................................................... 86
APPENDIX A SPECIFICATIONS ............................................................................................................................ 86
Wireless Access Point .................................................................................................................................... 86
APPENDIX B TROUBLESHOOTING ..................................................................................................................... 89
Ov e rvi ew .......................................................................................................................................................... 89
General Problems ........................................................................................................................................... 89
Page 4
P a g e 4 o f
9 3
C h a p t e r 1
I n t r o d u c t i o n
This Chapter provides an overview of the Wireless Access Point's features and capabilities.
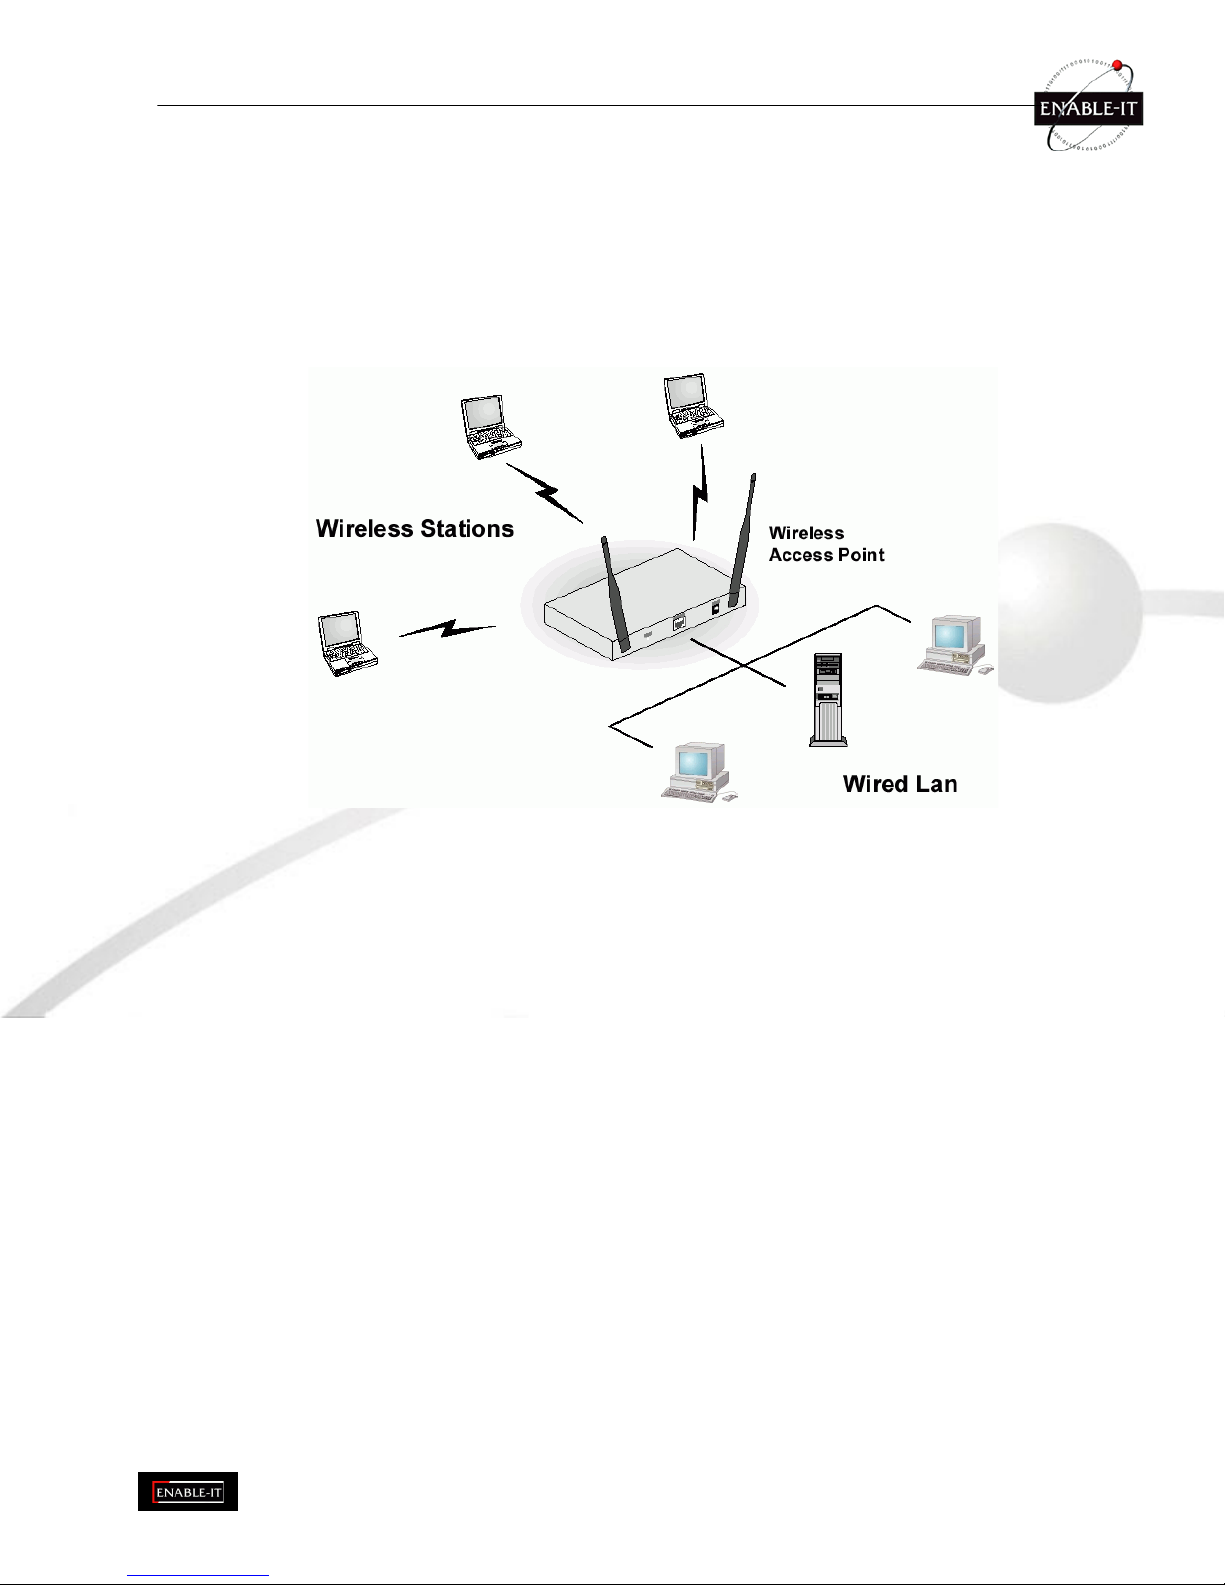
C o n g r a t u l a t i o n s o n t h e p u r c h a s e o f y o u r n e w W i r e l e s s A c c e s s P o i n t . T h e W i r e l e s s A c c e s s P o i n t l i n k s y o u r 8 0 2 . 1 1 g o r
8 0 2 . 1 1 b W i r e l e s s S t a t i o n s t o y o u r w i r e d L A N . T h e W i r e l e s s s t a t i o n s a n d d e v i c e s o n t h e w i r e d L A N a r e t h e n o n t h e s a m e
n e t w o r k , a n d c a n c o m m u n i c a t e w i t h e a c h o t h e r w i t h o u t r e g a r d f o r w h e t h e r t h e y a r e c o n n e c t e d t o t h e n e t w o r k v i a a
W i r e l e s s o r w i r e d c o n n e ct i o n .
Figure 1: Wireless Access Point
T h e a u t o -s e n s i n g c a p a b i l i t y o f t h e W i r e l e s s A c c e s s P o i n t a l l o w s p a c k e t t r a n s m i s s i o n u p t o 5 4 M b p s f o r m a x i m u m
t h r o u g h p u t , o r a u t o m a t i c s p e e d r e d u c t i o n t o l o w e r s p e e d s w h e n t h e e n v i r o n m e n t d o e s n o t p e r m i t m a x i m u m t h r o u g h p u t .
F e a t u r e s o f y o u r W i r e l e s s A c c e s s P o i n t
T h e W i r e l e s s A c c e s s P o i n t i n c o r p o r a t e s m a n y a d v a n c e d f e a t u r e s , c a r e f u l l y d e s i g n e d t o p r o v i d e s o p h i s t i c a t e d f u n c t i o n s
w h i l e b e i n g e a s y t o u s e .
•
Standards Compliant.
The Wireless Router complies with the IEEE802.11g (DSSS) specifications for Wireless
LANs.
•
Supports both 802.11b and 802.11g Wireless Stations.
The 802.11g standard provides for backward compatibility
with the 802.11b standard, so both 802.11b and 802.11g Wireless stations can be used simultaneously.
•
108Mbps Wireless Connections.
On both the 2.4GHz (802.11b & 802.11g) and 5GHz (802.11a) bands,
108Mbps connections are available to compatible clients.
•
Bridge Mode Support.
The Wireless Access Point can operate in Bridge Mode, connecting to another Access
Point. Both PTP (Point to Point) and PTMP (Point to Multi-Point) Bridge modes are supported.
And you can even use both Bridge Mode and Access Point Mode simultaneously!
•
Client/Repeater Access Point.
The Wireless Access Point can operate as a Client or Repeater Access Point,
sending all traffic received to another Access Point.
•
Simple Configuration.
If the default settings are unsuitable, they can be changed quickly and easily.
•
DHCP Client Support.
Dynamic Host Configuration Protocol provides a dynamic IP address to PCs and other
devices upon request. The Wireless Access Point can act as a DHCP Client, and obtain an IP address and
related information from your existing DHPC Server.
• Upgradeable Firmware. Firmware is stored in a flash memory and can be upgraded easily, using only your Web
Browser.
Page 5
P a g e 5 o f
9 3
S e c u r i t y F e a t u r e s
•
Security Profiles.
For maximum flexibility, wireless security settings are stored in Security Profiles. Up to 8
Security profiles can be defined, and up to 4 used as any time.
•
Multiple SSIDs.
Because each Security Profile has it own SSID, and up to 4 Security Profiles can be active
simultaneously, multiple SSIDs are supported. Different clients can connect to the Wireless Access Point
using different SSIDs, with different security settings.
•
Multiple SSID Isolation.
If desired, PCs and devices connecting using different SSIDs can be isolated from
each other.
•
VLAN Support.
The 802.1Q VLAN standard is supported, allowing traffic from different sources to be
segmented. Combined with the multiple SSID feature, this provides a powerful tool to control access to your
LAN.
•
WEP support.
Support for WEP (Wired Equivalent Privacy) is included. Both 64 Bit and 128 Bit keys are
supported.
•
WPA support.
Support for WPA is included. WPA is more secure than WEP, and should be used if possible.
Both TKIP and AES encryption methods are supported.
• 802.1x Support. Support for 802.1x mode is included, providing for the industrial-strength wireless security of
802.1x authentication and authorization.
• Radius Client Support. The Wireless Access Point can login to your existing Radius Server (as a Radius client).
• Radius MAC Authentication. You can centralize the checking of Wireless Station MAC addresses by using a
Radius Server.
• Rogue AP Detection. The Wireless Access Point can detect unauthorized (Rouge) Access Points on your LAN.
•
Access Control.
The Access Control feature can check the MAC address of Wireless clients to ensure that only
trusted Wireless Stations can use the Wireless Access Point to gain access to your LAN.
•
Password - protected Configuration
. Optional password protection is provided to prevent unauthorized users
from modifying the configuration data and settings.
A d v a n c e d F e a t u r e s
•
Auto Configuration.
The Wireless Access Point can perform self-configuration by copying the configuration data
from another Access Point. This feature is enabled by default.
•
Auto Update.
The Wireless Access Point can automatically update its firmware, by downloading and installing
new firmware from your FTP server.
•
Command Line Interface.
If desired, the command line interface (CLI) can be used for configuration. This
provides the possibility of creating scripts to perform common configuration changes.
•
NetBIOS & WINS Support.
Support for both NetBIOS broadcast and WINS (Windows Internet Naming Service)
allows the Wireless Access Point to easily fit into your existing Windows network.
•
Radius Accounting Support.
If you have a Radius Server, you can use it to provide accounting data on Wireless
clients.
•
Syslog Support.
If you have a Syslog Server, the Wireless Access Point can send its log data to your Syslog
Server.
•
SNMP Support.
SNMP (Simple Network Management Protocol) is supported, allowing you to use a SNMP
program to manage the Wireless Access Point.
• UAM Support. The
Wireless Access Point supports UAM (Universal Access Method), making it suitable for use
in Internet cafes and other sites where user access time must be accounted for.
• WDS Support. Support for WDS (Wireless Distribution System) allows the
Wireless Access Point to act as a
Wireless Bridge. Both Point-to-Point and Multi-Point Bridge modes are supported.
Page 6
P a g e 6 o f
9 3
P a c k a g e C o nt e n t s
T h e f o l l o w i n g i t e m s s h o u l d b e i nc l u d e d :
• Wireless Access Point
I f a n y o f t h e a b o v e i t e m s a r e d a m a g e d o r m i s s i n g , p l e a s e c o n t a c t y o u r d e a l e r i m m e d ia t e l y .
P h y s i c a l D e t a i l s
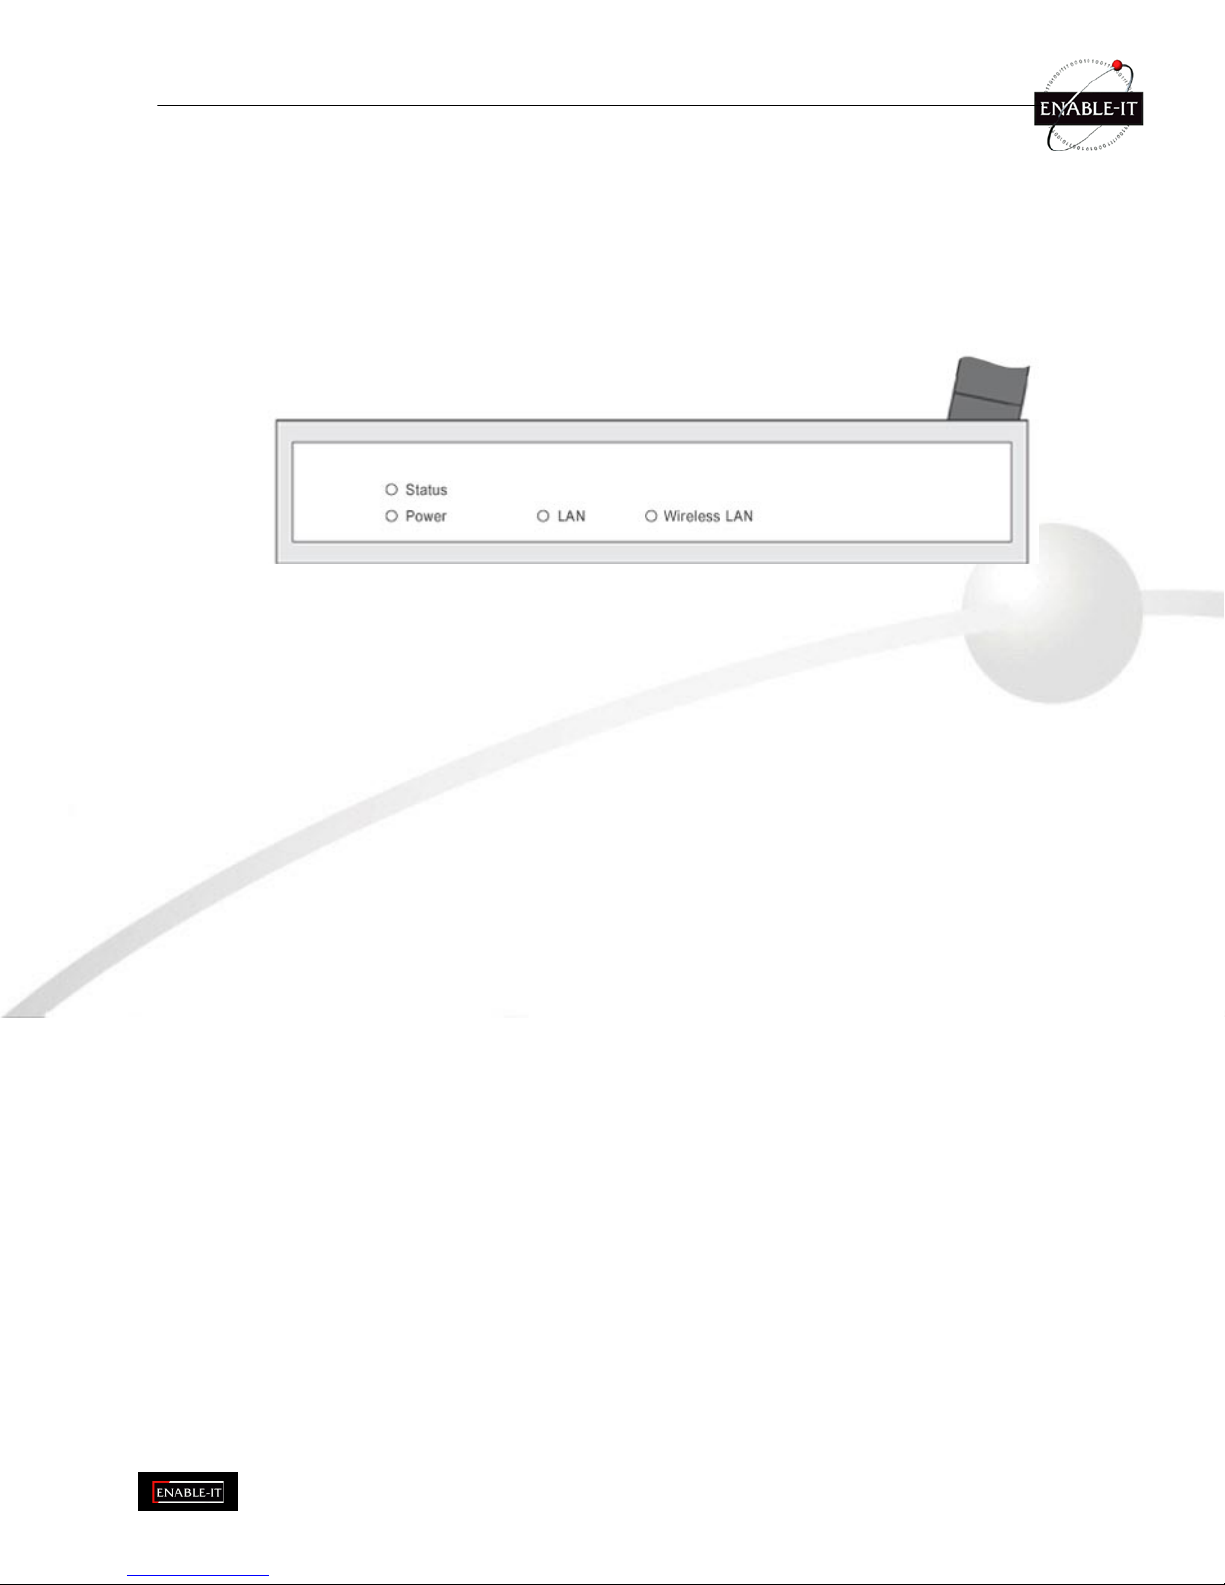
F r o n t P a n e l L E D s
Figure 2: Front Panel
S t a t u s
O n - E r r o r c o n d it i o n .
O f f - N o r m a l o p e r a t i o n .
B l i n k i n g - D u r i n g s t a r t u p , a n d w h e n t h e F i r m w a r e i s b e i n g u pg r a d e d .
P o w e r
O n - N o r m a l o p e r a t i o n .
O f f - N o p o w e r
L A N
O n - T h e L A N ( E t h e r n e t ) p o r t i s a c t i v e .
O f f - N o a c t i v e c o n n e c t i o n o n t h e L A N ( E t h e r n e t ) p o r t .
F l a s h i n g - D a t a i s b e i n g t r a n s m i t t e d o r r e c e i v e d v i a t h e c o r r es p o n d i n g
L A N ( E t h e r n e t ) p o r t .
W i r e l e s s
L A N
O n -
I d l e
O f f - E r r o r - W i r e l e s s c o n n e c t i o n i s n o t a v a i l a b l e .
F l a s h i n g - D a t a i s b e i n g t r a n s m i t t e d o r r e c e i v e d v i a t h e W i r e l e s s
a c c e s s p o i n t . D a t a i n c l u d e s " n e t w o r k t r a f f i c " a s w e l l a s u s e r d a t a .
Page 7
P a g e 7 o f
9 3
R e a r P a n e l
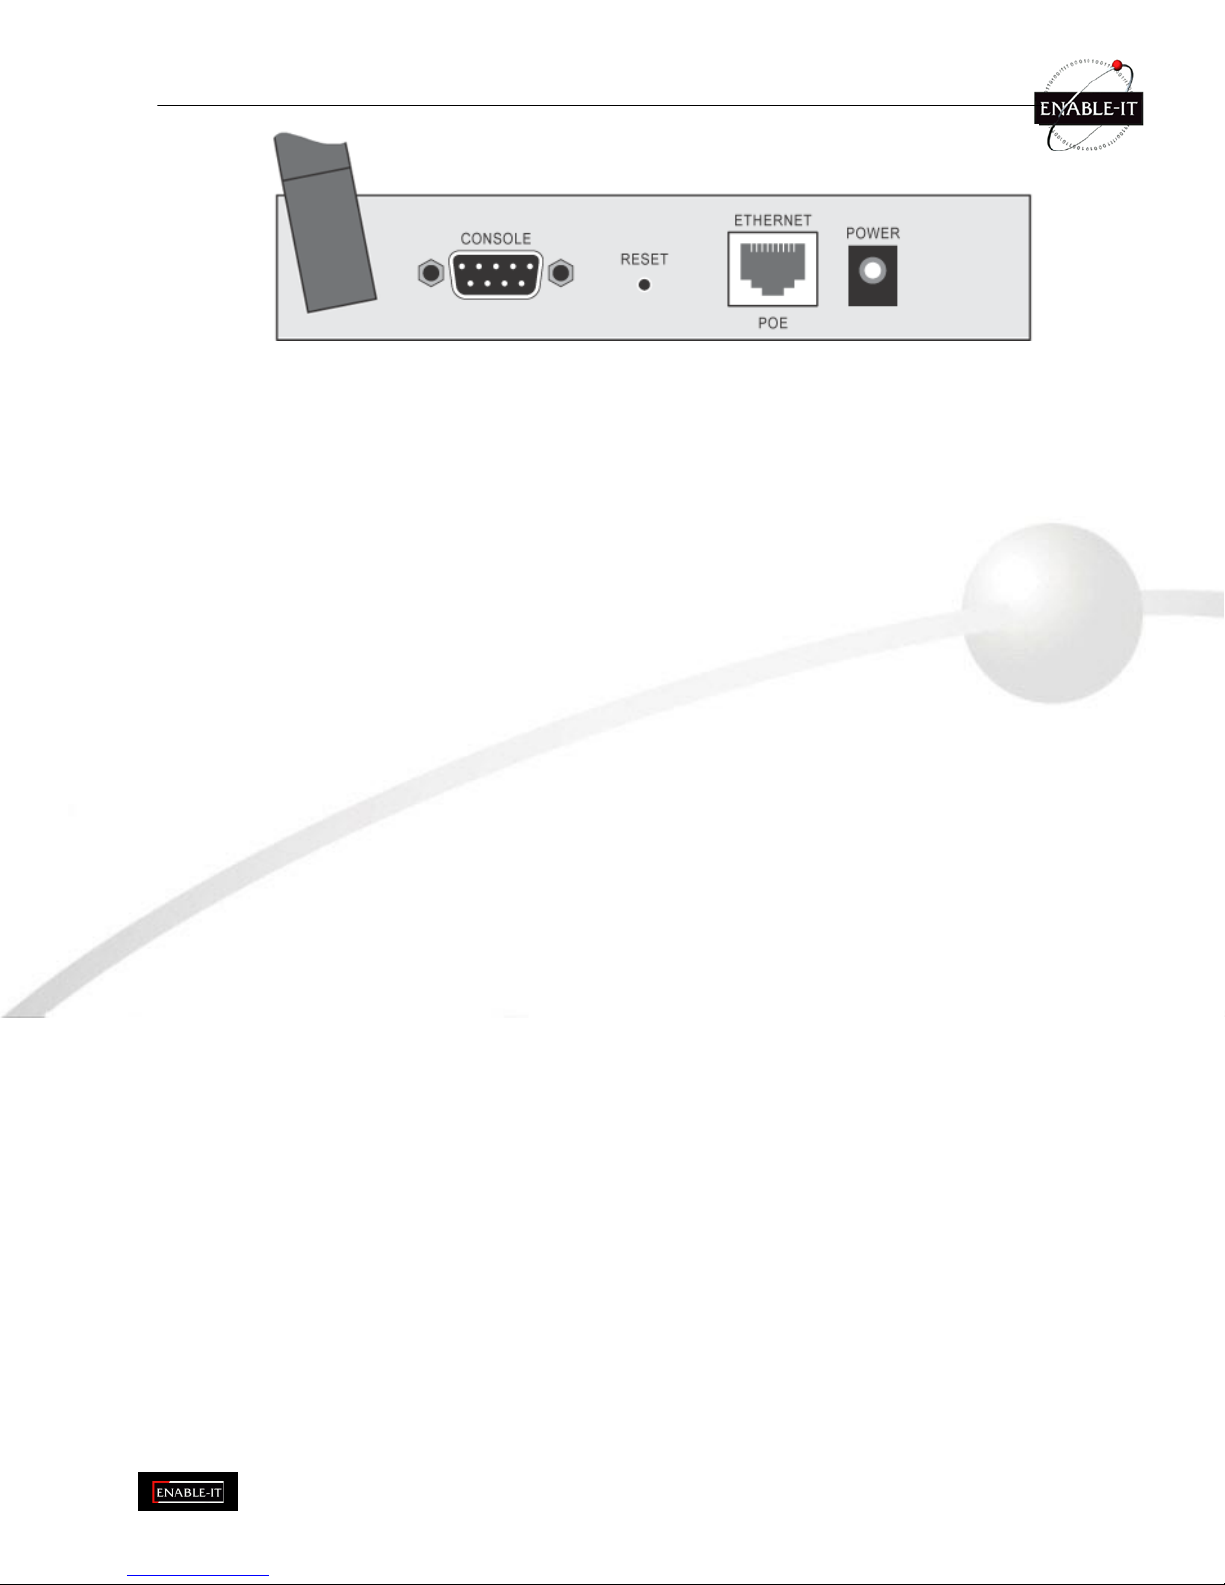
Figure 3 Rear Panel
A n t e n n a
O n e a n t e n n a ( a e r i a l ) i s s u p p l i e d . B e s t r e s u l t s a r e u s u a l l y o bt a i n e d
w i t h t h e a n t e n n a i n a v e r t i c a l p o s it i o n .
C o n s o l e p o r t
D B 9 f e m a l e R S 2 3 2 p o r t .
R e s e t B u t t o n
T h i s b u t t o n h a s t w o ( 2 ) f u n c t i o n s :
• Reboot. When pressed and released, the Wireless Access
Point will reboot (restart).
• Reset to Factory Defaults. This button can also be used to
clear ALL data and restore ALL settings to the factory
default values.
T o C l e a r A l l D a t a a n d r e s t o r e t h e f a c t o r y d e f a u l t v a l u e s :
1. Power Off the Access Point
2. Hold the Reset Button down while you Power On the Access
Point.
3. Continue holding the Reset Button until the Status (Red)
LED blinks TWICE.
4. Release the Reset Button.
The factory default configuration has now been restored,
and the Access Point is ready for use.
E t h e r n e t
U s e a s t a n d a r d L A N c a b l e ( R J 4 5 c o n n e c t o r s ) t o c o n n e c t t h i s p o r t t o
a 1 0 B a s e T o r 1 0 0 B a s e T h u b o n y o u r L A N .
P o w e r p o r t
C o n n e c t t h e s u p p l i e d p o w e r a d a p t e r h e r e .
Page 8
P a g e 8 o f
9 3
C h a p t e r 3
A c c e s s P o i n t S e t u p
This Chapter provides details of the Setup process for Basic Operation of your Wireless Access
Point.
O v e r v i e w
T h i s c h a p t e r d e s c r i b e s t h e s e t u p p r o c e d u r e t o m a k e t h e W i r e l e s s A c c e s s P o i n t a v a l i d d e v i c e o n y o u r L A N , a n d t o
f u n c t i o n a s a n A c c e s s P o i n t f o r y o u r W i r e l e s s S t a t i o n s .
W i r e l e s s S t a t i o n s m a y a l s o r e q u i r e c o n f i g u r a t i o n . F o r d e t a i l s , s e e C h a p t e r 4 - W i r e l e s s S t a t i o n C o n f i g u r a t i o n .
T h e W i r e l e s s A c c e s s P o i n t c a n b e c o n f i g u r e d u s i n g e i t h e r t h e s u p p l i e d W i n d o w s u t i l i t y o r y o u r W e b B r o w s e r
S e t u p u s i n g t h e W i n d o w s U t i l i t y
A s i m p l e W i n d o w s s e t u p u t i l i t y i s s u p p l i e d o n t h e C D -R O M . T h i s u t i l i t y c a n b e u s e d t o a s s i g n a s u i t a b l e I P a d d r e s s t o t h e
W i r e l e s s A c c e s s P o i n t . U s i n g t h i s u t i l i t y i s r e c o mm e n d e d , b e c a u s e i t c a n l o c a t e t h e W i r e l e s s A c c e s s P o i n t e v e n i f i t h a s
a n i n v a l i d I P a d d r e s s .
I n s t a l l a t i o n
5. Insert the supplied CD-ROM in your drive.
6. If the utility does not start automatically, run the SETUP program in the root folder.
7. Follow the prompts to complete the installation.
M a i n S c r e e n
• Start the program by using the icon created by the setup program.
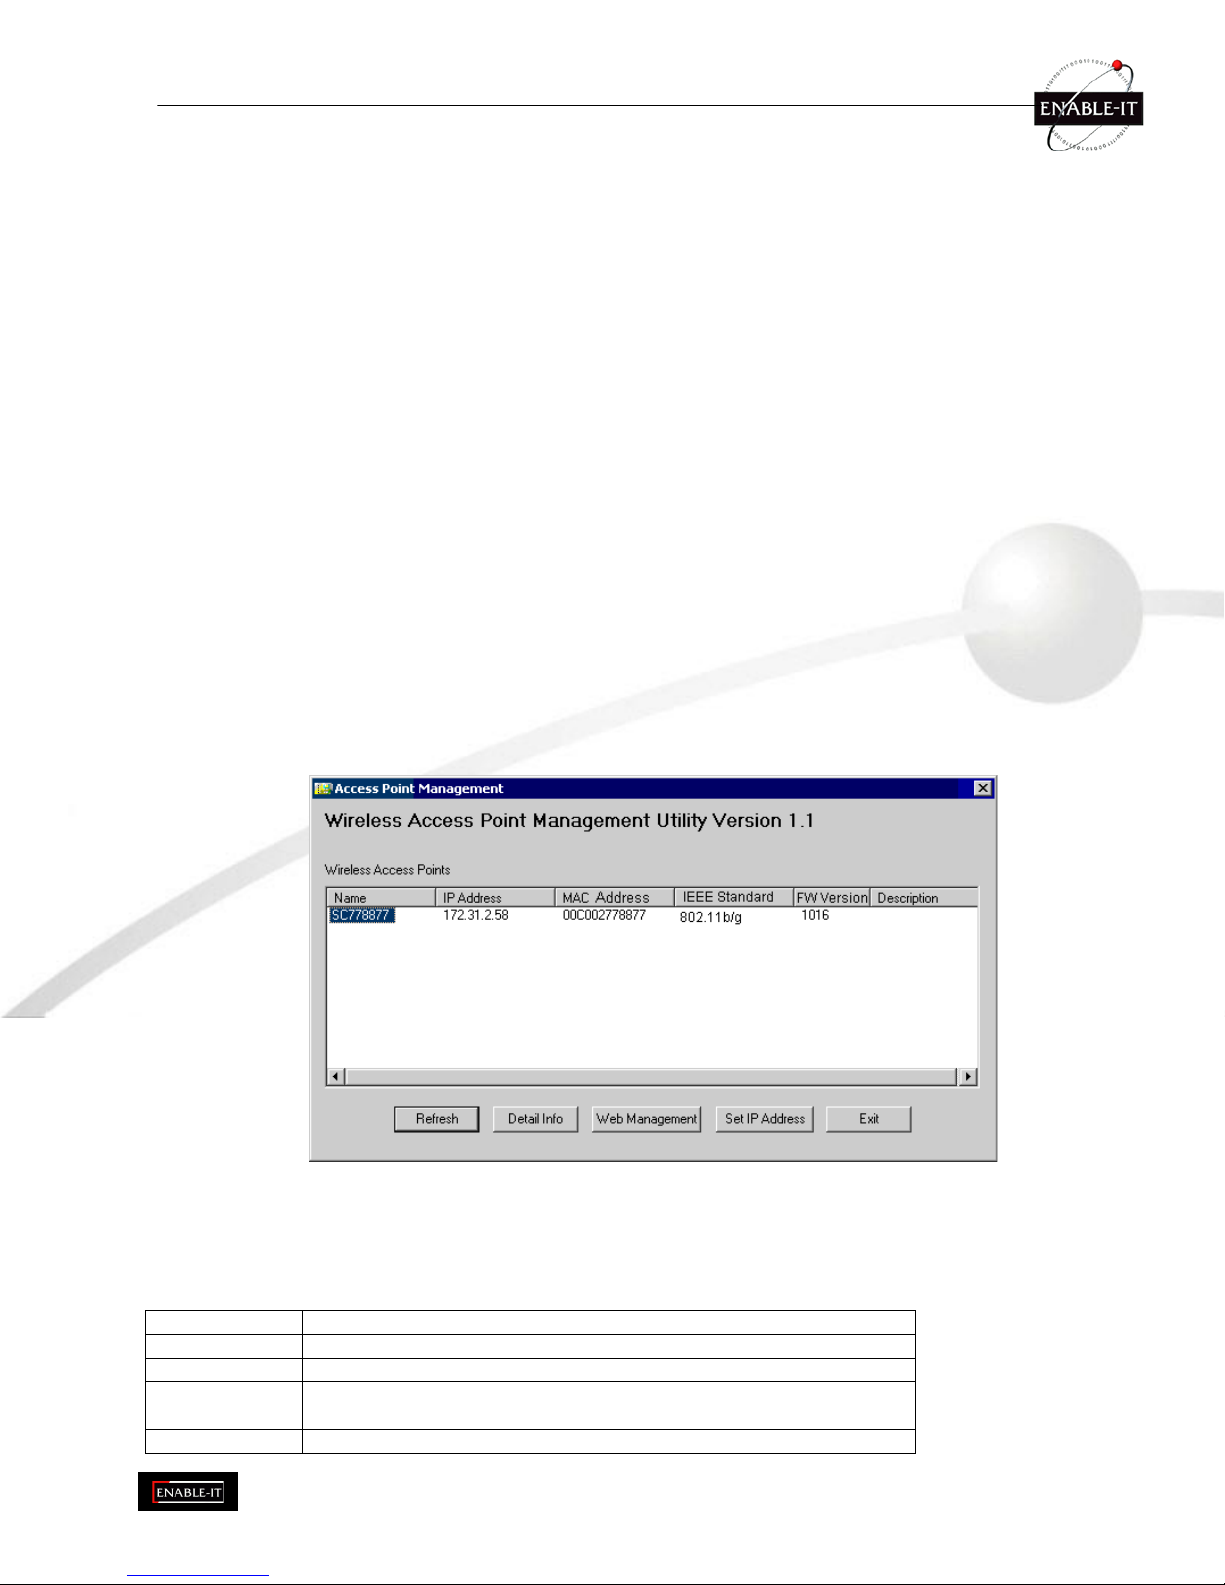
• When run, the program searches the network for all active Wireless Access Points, then lists them on screen,
as shown by the example below.
Figure 4: Management utility Screen
Wireless Access Points
T h e m a i n p a n e l d i s p l a y s a l i s t o f a l l W i r e l e s s A c c e s s P o i n t s f o u n d o n t h e n e tw o r k . F o r e a c h A c c e s s P o i n t , t h e f o l l o w i n g
d a t a i s s h o w n :
S e r v e r N a m e
T h e S e r v e r N a m e i s s h o w n o n a s t i c k e r o n t h e b a s e o f t h e d e v i c e .
I P a d d r e s s
T h e I P a d d r e s s f o r t h e W i r e l e s s A c c e s s P o i n t .
M A C A dd r e s s
T h e h a r d w a r e o r p h y s i c a l a d d r e s s o f t h e W i r e l e s s A c c e s s P o i n t .
I E E E S t a nd a r d
T h e w i r e l e s s s t a n d a r d o r s t a n d a r d s u s e d b y t h e W i r e l e s s A c c e s s
P o i n t ( e . g . 8 0 2 . 1 1 b , 8 0 2 . 1 1 g )
F W V e r s i o n
T h e c u r r e n t F i r m w a r e v e r s i o n i n s t a l l e d i n t h e W i r e l e s s A c c e s s P o i n t .
Page 9
P a g e 9 o f
9 3
D e s c r i p t i o n
A n y e x t r a i n f o r m a t i o n f o r t h e W i r e l e s s A c c e s s P o i n t , e n t e r e d b y t h e
a d m i n i s t r a t o r .
N o t e : I f t h e d e s i r e d W i r e l e s s A c c e s s P o i n t i s n o t l i s t e d , c h e c k t h a t t h e d e v i c e i s i n s t a l l e d a n d O N , t h e n u p d a t e t h e l i s t b y
c l i c k i n g t h e R e f r e s h b u t t o n .
Buttons
R e f r e s h
C l i c k t h i s b u t t o n t o u p d a t e t h e W i r e l e s s A c c e s s P o i n t d e v i c e
l i s t i n g a f t e r c h a n gi n g t h e n a m e o r I P A d d r e s s .
D e t a i l I n f o
W h e n c l i c k e d , a d d i t i o n a l i n f o r m a t i o n a b o u t t h e s e l e c t e d A c c e s s
P o i n t w i l l b e d i s p l a y e d .
W e b M a n a g em e n t
U s e t h i s b u t t o n t o c o n n e c t t o t h e W i r e l e s s A c c e s s P o i n t ' s W e b b a s e d m a n a g e m e n t i n t e r f a c e .
S e t I P A d d r e s s
C l i c k t h i s b u t t o n i f y o u w a n t t o c h a n g e t h e I P A d d r e s s o f t h e
W i r el e s s A c c e s s P o i n t .
E x i t
E x i t t h e M a n a g e m e n t u t i l i t y p r o g r a m b y c l i c k i n g t h i s b u t t o n .
Page 10
P a g e 1 0 o f
9 3
Se t u p P r o c e d u r e
8. Select the desired Wireless Access Point.
9. Click the Set IP Address button.
10. If prompted, enter the user name and password. The default values are admin for the User Name, and
password for the Password.
11. Ensure the IP address, Network Mask, and Gateway are correct for your LAN. Save any changes.
12. Click the Web Management button to connect to the selected Wireless Access Point using your Web
Browser. If prompted, enter the User Name and Password again.
13. Check the following screens, and configure as necessary for your environment. Use the on-line help if
necessary.
The later sections in this Chapter also provides more details about each of these screens.
• Access Control - MAC level access control.
• Security Profiles - Wireless security.
• System - Identification, location, and Network settings
• Wireless - Basic & Advanced
14. You may also wish to set the admin password and administration connection options. These are on the Admin
Login screen accessed from the Management menu. See Chapter 6 for details of the screens and features
available on the Management menu.
15. Use the Apply/Restart button on the menu to apply your changes and restart the Wireless Access Point.
S e t u p i s n o w c o mp l e t e .
W i r e l e s s s t a t i o n s m u s t n o w b e s e t t o m a t c h t h e W i r e l e s s A c c e s s P o i n t . S e e C h a p t e r 4 f o r d e t a i l s .
S e t u p u s i n g a W e b B r o w s e r
Y o u r B r o w s e r m u s t s u p p o r t J a v a S c r i p t . T h e c o n f i g u r a t i o n p r o g r a m h a s b e e n t e s t e d o n t h e f o l l o w i n g b r o w se r s :
• Netscape V4.08 or later
• Internet Explorer V4 or later
S e t u p P r o c e d u r e
B e f o r e c o m m e n c i n g , i n s t a l l t h e W i r e l e s s A c c e s s P o i n t i n y o u r L A N , a s d e s c r i b e d p r e v i o u s l y .
16. Check the Wireless Access Point to determine its Default Name. This is shown on a label on the base or rear,
and is in the following format:
SCxxxxxx
Where xxxxxx is a set of 6 Hex characters ( 0 ~ 9, and A ~ F ).
17. Use a PC which is already connected to your LAN, either by a wired connection or another Access Point.
• Until the Wireless Access Point is configured, establishing a Wireless connection to it may be not
possible.
• If your LAN contains a Router or Routers, ensure the PC used for configuration is on the same LAN
segment as the Wireless Access Point.
18. Start your Web browser.
19. In the Address box, enter HTTP:// and the Default Name of the Wireless Access Point
e.g.
H T T P : / / S C 2 D 6 3 1 A
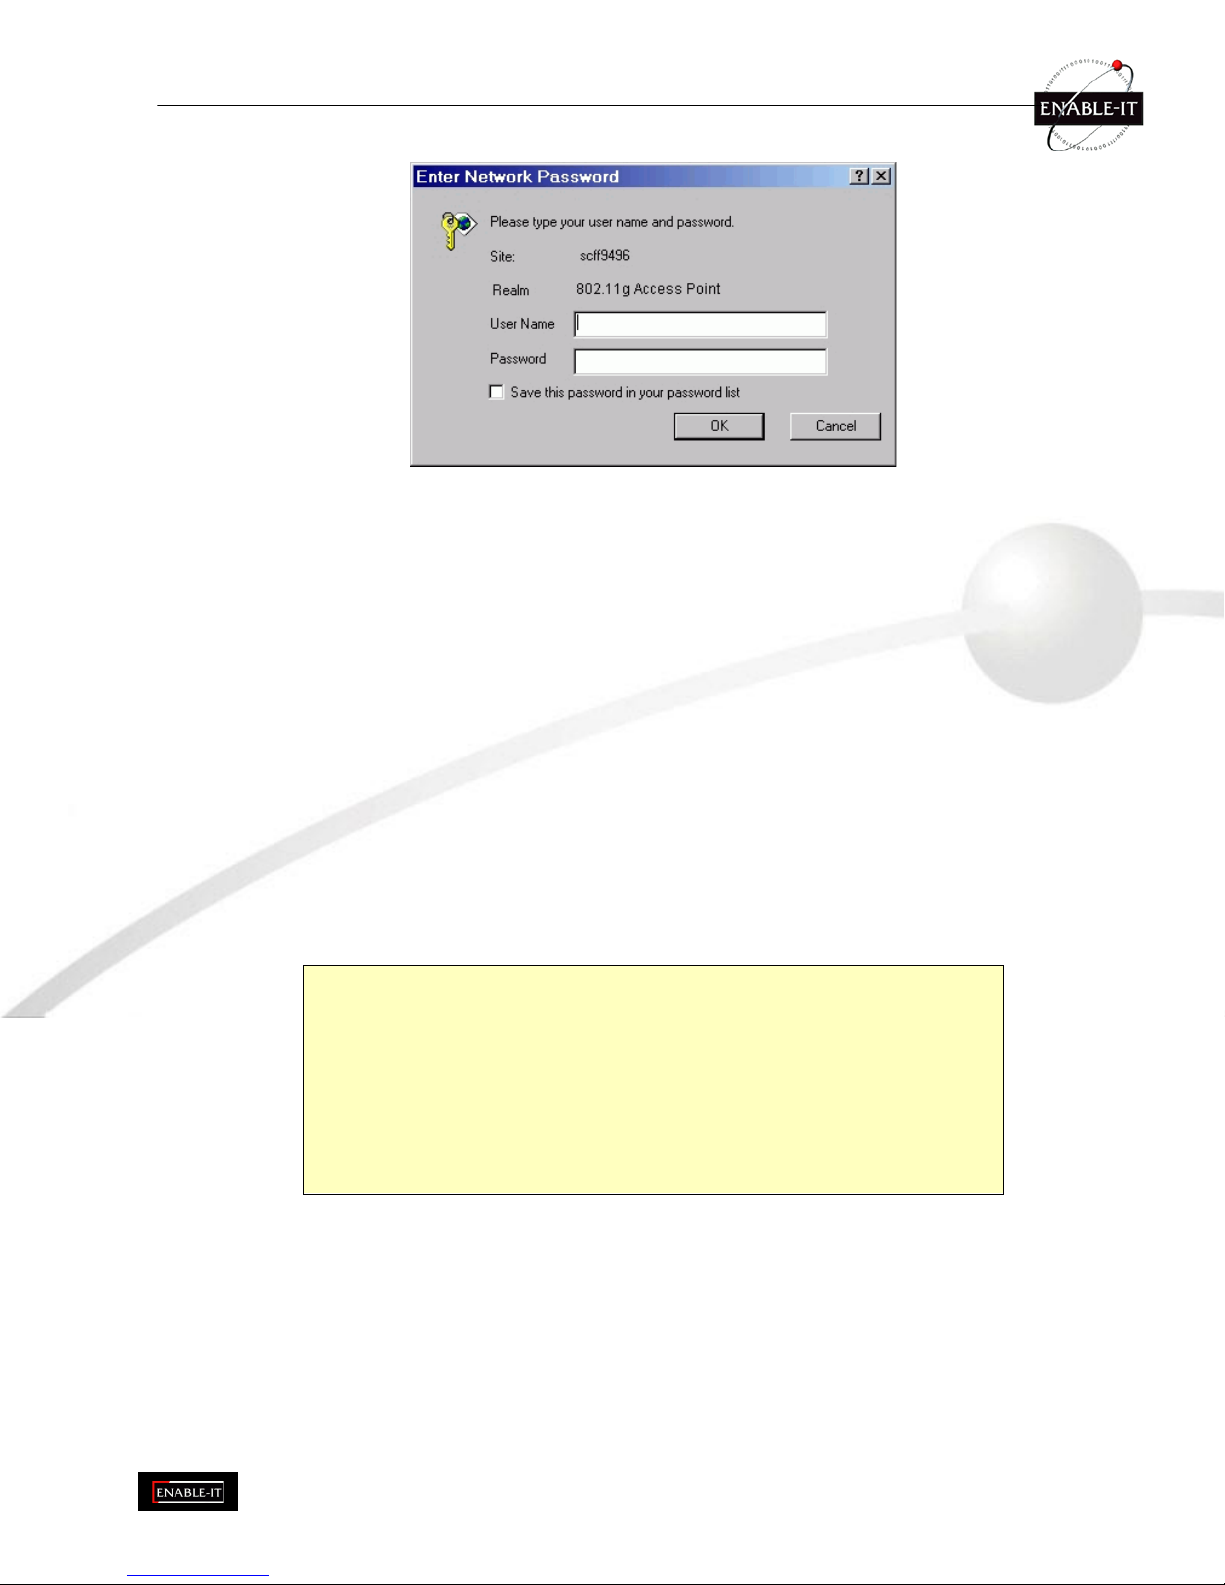
20. You should then see a login prompt, which will ask for a User Name and Password.
Enter admin for the User Name, and password for the Password.
These are the default values. The password can and should be changed. Always enter the current user name
and password, as set on the Admin Login screen.
Page 11
P a g e 1 1 o f
9 3
Figure 5: Password Dialog
21. You will then see the Status screen, which displays the current settings and status. No data input is possible
on this screen. See Chapter 5 for details of the Status screen.
From the menu, check the following screens, and configure as necessary for your environment. Details of these
screens and settings are described in the following sections of this chapter.
• Access Control - MAC level access control.
• Security Profiles - Wireless security.
• System - Identification, location, and Network settings
• Wireless - Basic & Advanced
22. You may also wish to set the admin password and administration connection options. These are on the Admin
Login screen accessed from the Management menu. See Chapter 6 for details of the screens and features
available on the Management menu.
23. Use the Apply/Restart button on the menu to apply your changes and restart the Wireless Access Point.
S e t u p i s n o w c o mp l e t e .
W i r e l e s s s t a t i o n s m u s t n o w b e s e t t o m a t c h t h e W i r e l e s s A c c e s s P o i n t . S e e C h a p t e r 4 f o r d e t a i l s .
If you can't connect:
I t i s l i k e l y t h a t y o u r P C ’ s I P a d d r e s s i s i n c o m p a t i b l e w i t h t h e W i r e l e s s A cc e s s
P o i n t ’ s I P a d d r e s s . T h i s c a n h a p p e n i f y o u r L A N d o e s n o t h a v e a D H C P S e r v e r .
T h e d e f a u l t I P a d d r e s s o f t h e W i r e l e s s A c c e s s P o i n t i s 1 9 2 . 1 6 8 . 0 . 2 2 8 , w i t h a
N e tw o r k M a s k o f 2 5 5 . 2 5 5 . 2 5 5 . 0 .
I f y o u r P C ’ s I P a d d r e s s i s n o t c o m p a t i b l e w i t h t h i s , y o u m u s t c h a n g e y o u r P C ’ s
I P a d d r e s s t o a n u n u s e d v a l u e i n t h e r a n g e 1 9 2 . 1 6 8 . 0 . 1 ~ 1 9 2 . 1 6 8 . 0 . 2 5 4 , w i t h a
N e tw o r k M a s k o f 2 5 5 . 2 5 5 . 2 5 5 . 0 . S e e A p p e n d i x C - W i n d o w s T C P / I P f o r
d e t a i l s f o r t h i s p r o c ed u r e .
Page 12
P a g e 1 2 o f
9 3
A c c e s s C o n t r o l
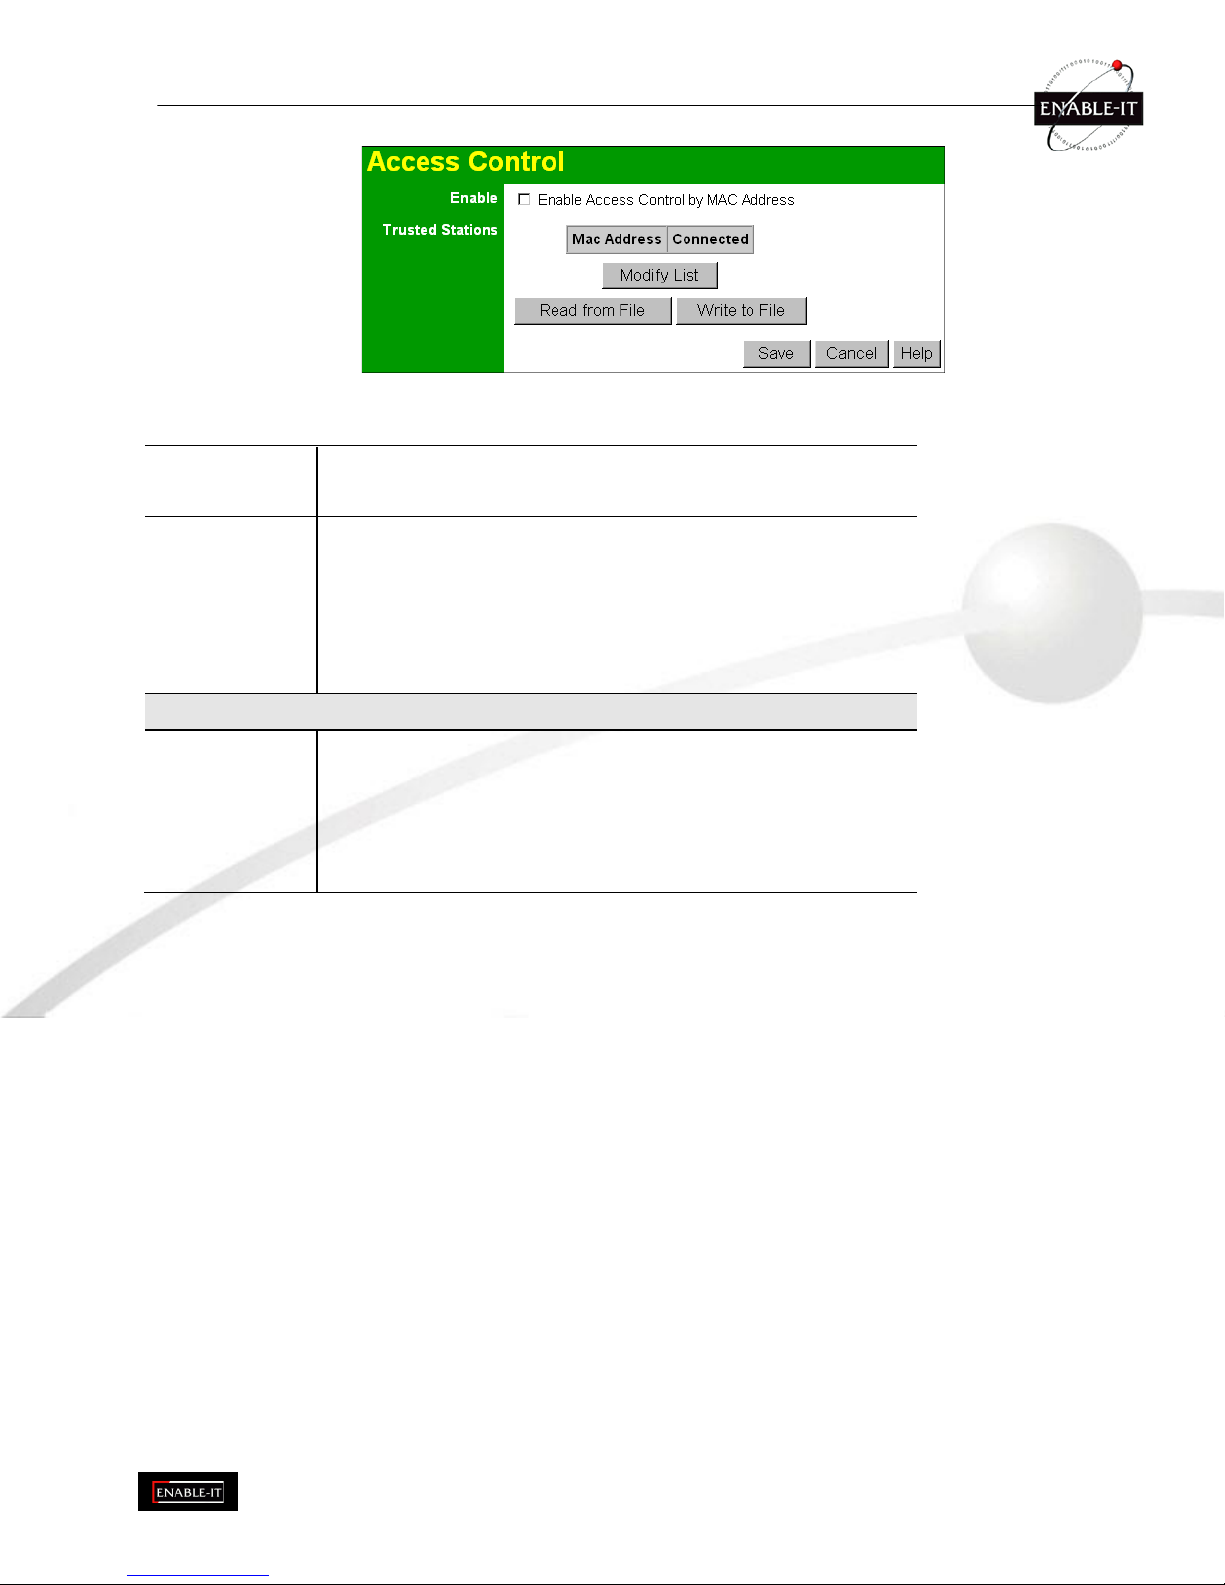
T h i s f e a t u r e c a n b e u s e d t o b l o c k a c c e s s t o y o u r L A N b y u n k n o w n o r u n t r u s t e d w i r el e s s s t at i o n s .
C l i c k A c c e s s C o n t r o l o n t h e m e n u t o v i e w a s c r e e n l i k e t h e f o l l o wi n g .
Figure 6: Access Control Screen
D a t a - A c c e s s C o n t r o l S c r e e n
E n a b l e
U s e t h i s c h e c k b o x t o E n a b l e o r D i s a b l e t h i s f e a t u r e a s d e s i r e d .
W a r n i n g ! E n s u r e y o u r o w n P C i s i n t h e " T r u s t e d W i r e l e s s S t a t i o n s "
l i s t b e f o r e e n a b l i n g t h i s f e a t u r e .
T r u s t e d
S t at i o n s
T h i s t a b l e l i s t s a n y W i r e l e s s S t a t i o n s y o u h a v e d e s i g n a t e d a s
" T r u s t e d " . I f y o u h a v e n o t a d d e d a n y s t a t i o n s , t h i s t a b l e w i l l b e
e m p t y . F o r e a c h W i r e l e s s s t a t i o n , t h e f o l l o w i n g d a t a i s d i s p l a y e d :
• MAC Address - the MAC or physical address of each
Wireless station.
• Connected - this indicates whether or not the Wireless
station is currently associates with this Access Point.
Buttons
M o d i f y L i s t
T o c h a n g e t h e l i s t o f T r u s t e d S t a t i o n s ( A d d , E d i t , o r D e l e t e a
W i r e l e s s S t a t i o n o r S t a t i o n s ) , c l i c k t h i s b u t t o n . Y o u w i l l t h e n s e e t h e
T r u s t e d W i r e l e s s S t a t i o n s s c r e e n , d e s c r i b e d b e l o w .
R e a d f r o m F i l e
T o u p l o a d a l i s t o f T r u s t e d S t a t i o n s f r o m a f i l e o n y o u r P C , c l i c k t h i s
b u t t o n .
W r i t e t o F i l e
T o d o w n l o a d t h e c u r r e n t l i s t o f T r u s t e d S t a t i o n s f r o m t h e A c c e s s
P o i n t t o a f i l e o n y o u r P C , c l i c k t h i s b u t t o n .
Page 13
P a g e 1 3 o f
9 3
T r u s t e d W i r e l e s s S t a t i o n s
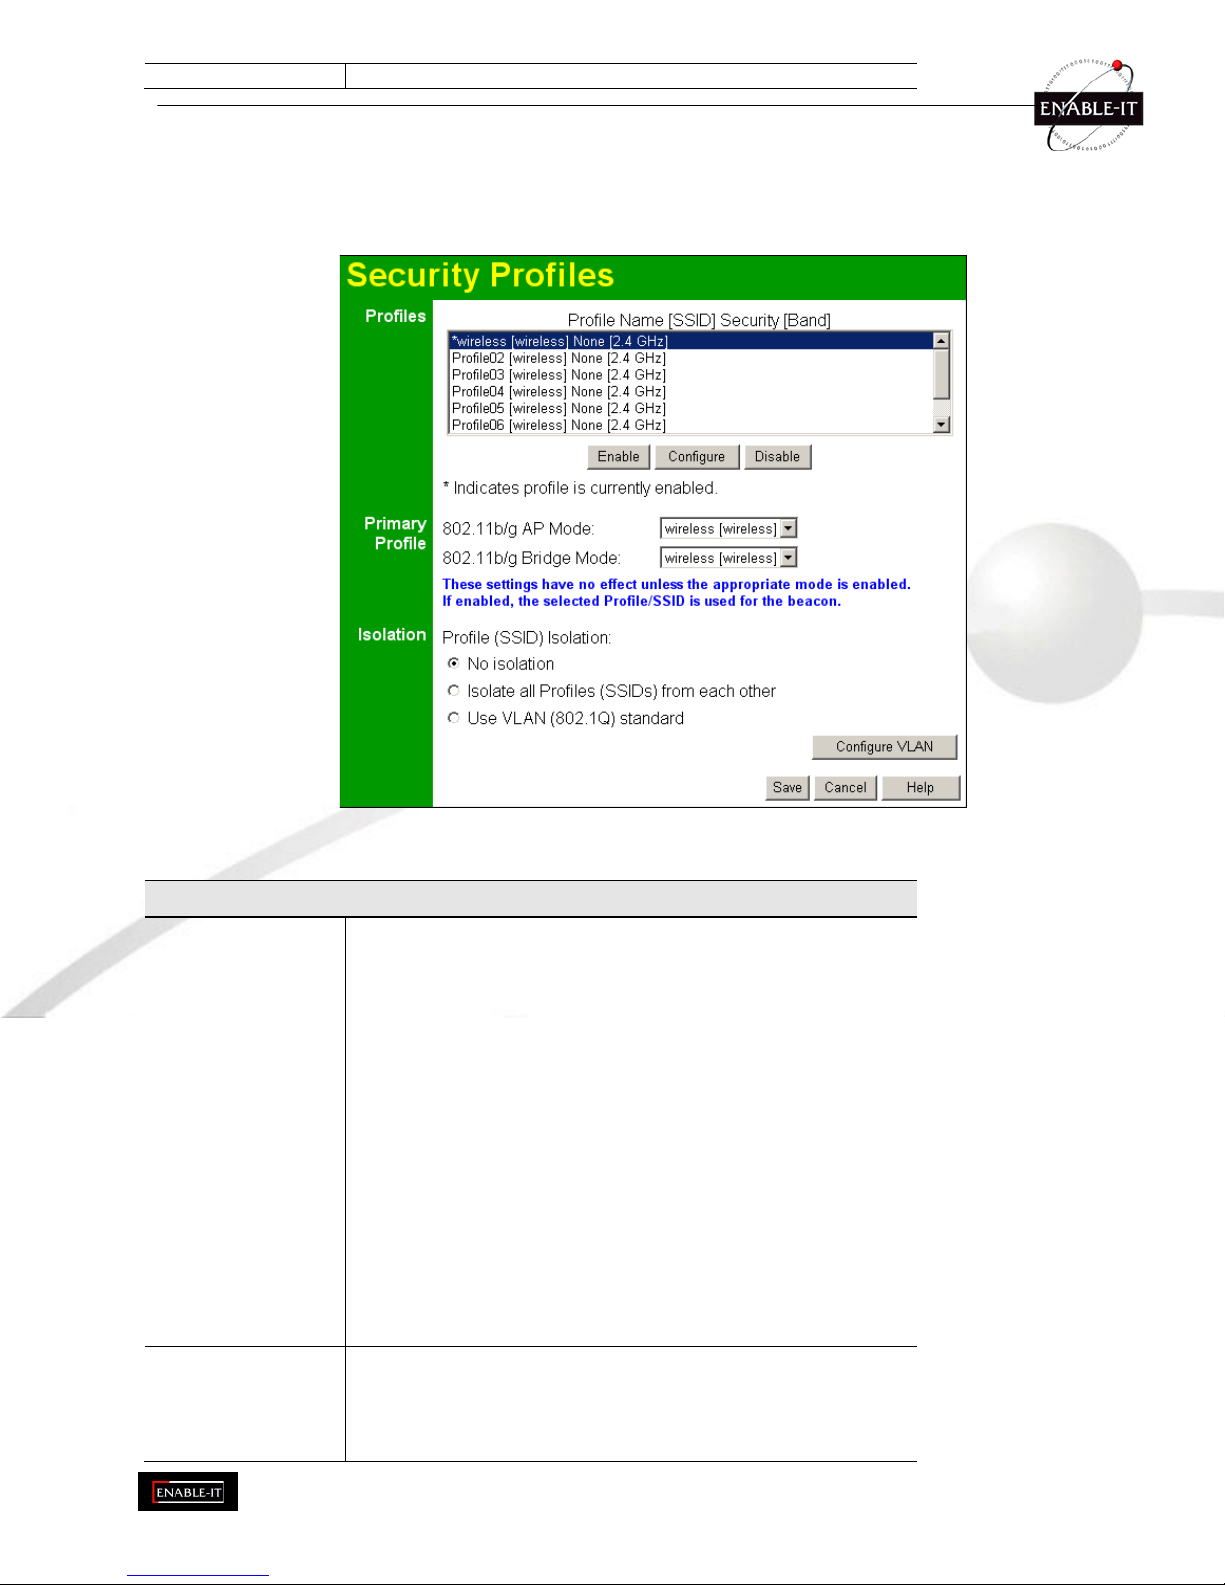
T o c h a n g e t h e l i s t o f t r u s t e d w i r e l e s s s t at i o n s , u s e t h e M o d i f y L i s t b u t t o n o n t h e Acc e s s C o n t r o l s c r e e n . Y o u w i l l s e e a
s c r e e n l i k e t h e s a m p l e b e l o w .
Figure 7: Trusted Wireless Stations
D a t a - T r u s t e d W i r e l e s s S t a t i o n s
T r u s t e d W i r e l e s s
S t a t i o n s
T h i s l i s t s a n y W i r e l e s s S t a t i o n s w h i c h y o u h a v e d e s i g n a t e d a s
“ T r u s t e d ” .
O t h e r W i r e l e s s
S t a t i o n s
T h i s l i s t a n y W i r e l e s s S t a t i o n s d e t e c t e d b y t h e A c c e s s P o i n t ,
w h i c h y o u h a v e n o t d e s i g n a t e d a s " T r u s t e d " .
N a m e
T h e n a m e a s s i g n e d t o t h e T r u s t e d W i r e l e s s S t a t i o n . U s e t h i s
w h e n a d d i n g o r e d i t i n g a T r u s t e d S t a t i o n .
A d d r e s s
T h e M A C ( p h y s i c a l ) a d d r e s s o f t h e T r u s t e d W i r e l e s s S t a t i o n .
U s e t h i s w h e n a d d i n g o r e d i t i n g a T r u s t e d S t a t i o n .
Buttons
< <
A d d a T r u s t e d W i r e l e s s S t a t i o n t o t h e l i s t ( m o v e f r o m t h e " O t h e r
S t a t i o n s " l i s t ) .
• Select an entry (or entries) in the "Other Stations" list,
and click the " << " button.
• Enter the Address (MAC or physical address) of the
wireless station, and click the "Add " button.
> >
D e l e t e a T r u s t e d W i r e l e s s S t a t i o n f r o m t h e l i s t ( m o v e t o t h e
" O t h e r S t a t i o n s " l i s t ) .
• Select an entry (or entries) in the "Trusted Stations" list.
• Click the " >> " button.
S e l e c t A l l
S e l e c t a l l o f t h e S t a t i o n s l i s t e d i n t h e " O t h e r S t a t i o n s " l i s t .
S e l e c t N o n e
D e -s e l e c t a n y S t a t i o n s c u r r e n t l y s e l e c t e d i n t h e " O t h e r S t at i o n s "
l i s t .
E d i t
To change an existing entry in the "Trusted Stations" list,
select it and click this button.
24. Select the Station in the "Trusted Station" list.
25. Click the "Edit" button. The address will be copied to the
"Address" field, and the "Add" button will change to
"Update".
26. Edit the address (MAC or physical address) as required.
27. Click "Update" to save your changes.
A d d
T o a d d a T r u s t e d S t a t i o n w h i c h i s n o t i n t h e " O t h e r W i r e l e s s
S t at i o n s " l i s t , e n t e r t h e r e q u i r e d d a t a a n d c l i c k t h i s b u t t o n .
Page 14
P a g e 1 4 o f
9 3
C l e a r
C l e a r t h e N a m e a n d A d d r e s s f i e l d s .
S e c u r i t y P r o f i l e s
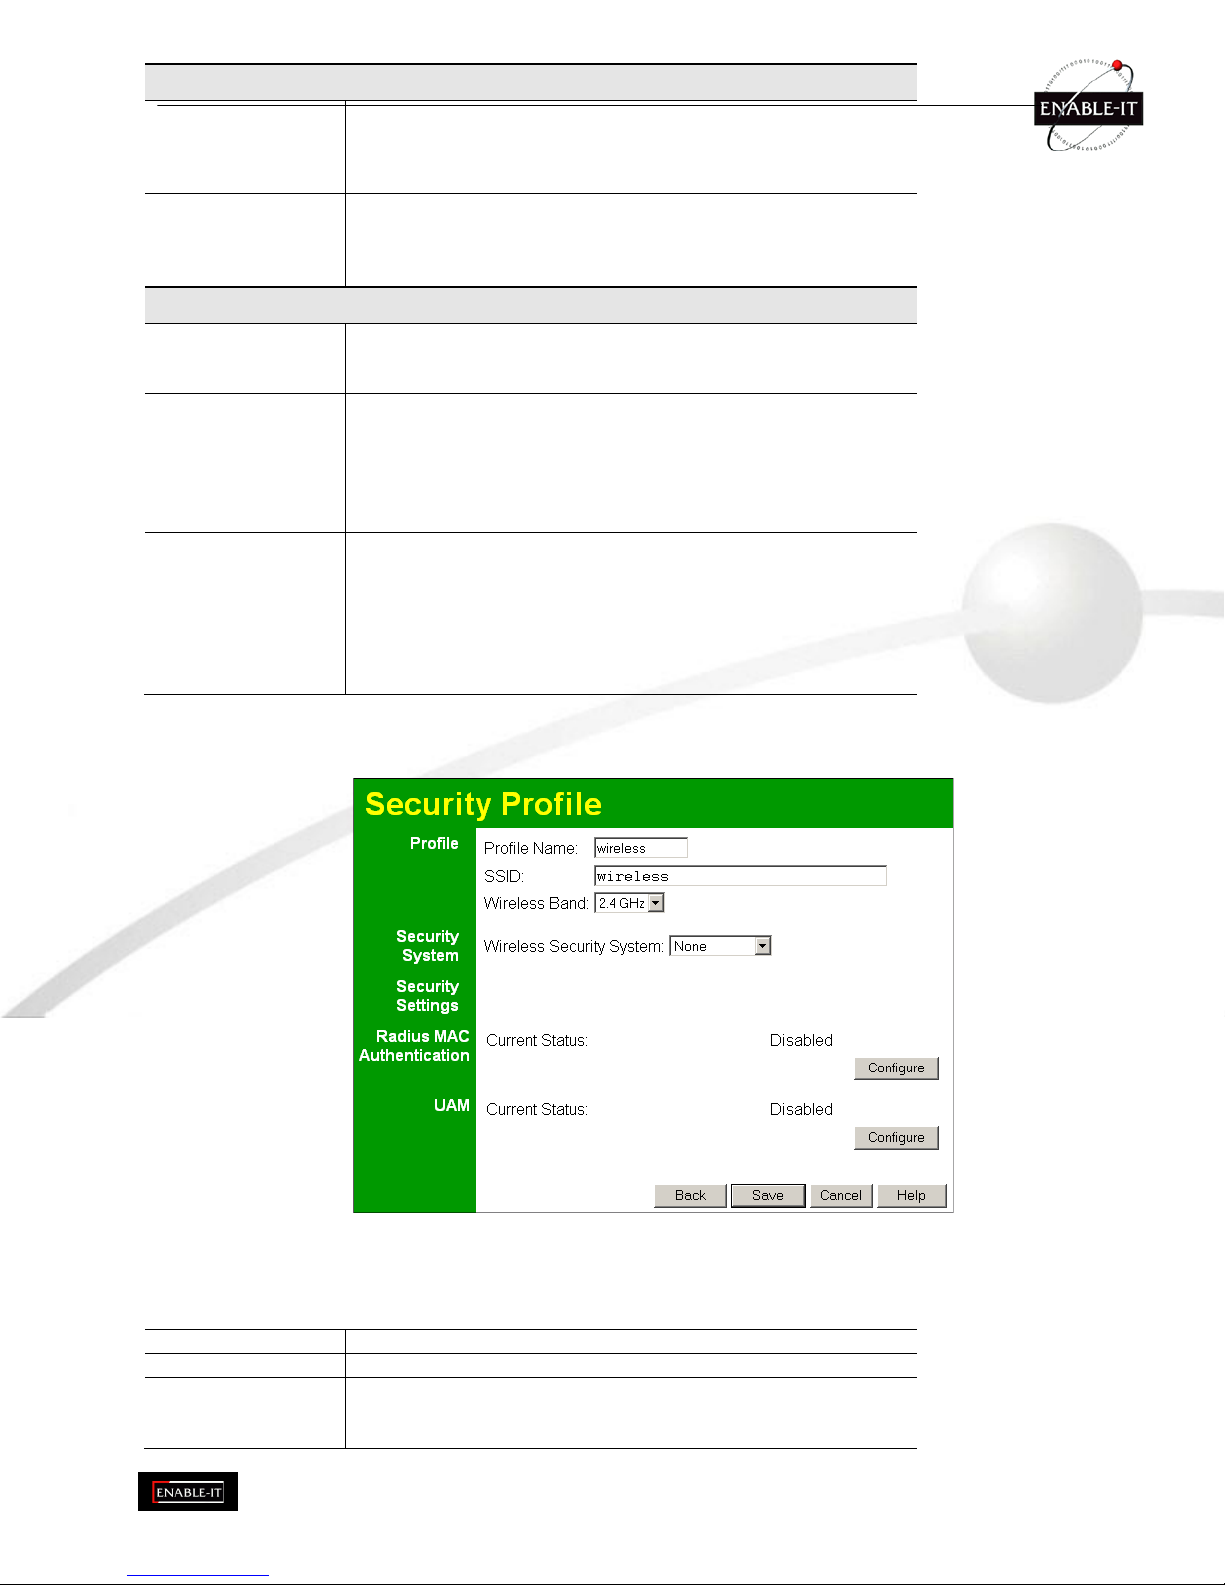
S e c u r i t y P r o f i l e s c o n t a i n t h e S S I D a n d a l l t h e s e c u r i t y s e t t i n g s f o r W i r e l e s s c o n n e ct i o n s t o t h i s A c c e s s P o i n t .
• Up to eight (8) Security Profiles can be defined.
• Up to four (4) Security Profiles can be enabled at one time, allowing up to 4 different SSIDs to be used
simultaneously.
Figure 8: Security Profiles Screen
D a t a - S e c u r i t y P r o f i l e s S c r e e n
Profile
P r o f i l e L i s t
A l l a v a i l a b l e p r o f i l e s a r e l i s t e d . F o r e a c h p r o f i l e , t h e f o l l o w i n g d a t a
i s d i s p l a y e d :
• *
If displayed before the name of the profile, this indicates
the profile is currently enabled. If not displayed, the
profile is currently disabled.
• Profile Name
The current profile name is displayed.
• [SSID]
The current SSID associated with this profile.
• Security System
The current security system (e.g. WPA-PSK ) is
displayed.
• [Band]
The Wireless Band (2.4 GHz, 5GHz) for this profile is
displayed. Profiles may be assigned to either or both
Wireless Bands.
B u t t o n s
• Enable - Enable the selected profile.
• Configure - Change the settings for the selected profile.
• Disable - Disable the selected profile.
Page 15
P a g e 1 5 o f
9 3
Primary Profile
8 0 2 . 1 1 b / g A P M o d e
S e l e c t t h e p r i m a r y p r o f i l e f o r 8 0 2 . 1 1 b a n d 8 0 2 . 1 1 g ( 2 . 4 G H z
b a n d ) A P m o d e . O n l y e n a b l e d p r o f i l e s a r e l i s t e d . T h e S S I D
a s s o c i a t e d w i t h t h i s p r o f i l e w i l l b e b r o a d c a s t i f t h e " B r o a d c a s t
S S I D " s e t t i n g o n t h e Bas i c s c r e e n i s e n a b l e d .
8 0 2 . 1 1 b / g B r i d g e
M o d e
S e l e c t t h e p r i m a r y p r o f i l e f o r 8 0 2 . 1 1 b a n d 8 0 2 . 1 1 g ( 2 . 4 G H z
b a n d ) B r i d g e M o d e . T h i s s e t t i n g d e t e r m i n e s t h e S S I D a n d
s e c u r i t y s e tt i n g s u s e d f o r t h e B r i d g e c o n n e c t i o n t o t h e r e m o t e
A P .
Isolation
N o n e
I f t h i s o p t i o n i s s e l e c t e d , w i r e l e s s c l i e n t s u s i n g d i ff e r e n t p r o f i l e s
( d i f f e r e n t S S I D s ) a r e n o t i s o l a t e d f r o m e a c h o t h e r , s o t h e y w i l l b e
a b l e t o c o m m u n i c a t e w i t h e a c h o t h e r .
I s o l a t e a l l
I f t h i s o p t i o n i s s e l e c t e d , w i r e l e s s c l i e n t s u s i n g d i ff e r e n t p r o f i l e s
( d i f f e r e n t S S I D s ) a r e i s o l a t e d f r o m e a c h o t h e r , s o t h e y w i l l N O T
b e a b l e t o c o m m u n ic a t e w i t h e a c h o t h e r . T h e y w i l l s t i l l b e a b l e t o
c o m m u n i c a t e w i t h o t h e r c l i e n t s u s i n g t h e s a m e p r of i l e , u n l e s s t h e
" W i r e l e s s S e p a r a t i o n " s e t t i n g o n t h e " A d v a n c e d " s c r e e n h a s
b e e n e n a b l e d .
U s e V L A N
T h i s o p t i o n i s o n l y u s e f u l i f t h e h u b s / s w i t c h e s o n y o u r L A N
s u pp o r t t h e V L A N ( 8 0 2 . 1 Q ) s t a n d a r d .
W h e n V L A N i s u s e d , y o u m u s t s e l e c t t h e d e s i r e d V L A N f o r e a c h
s e c u r i t y p r o f i l e w h e n c o n f i g u r i n g t h e p r o f i l e . ( I f V L A N i s n o t
s e l e c t e d , t h e V L A N s e tt i n g f o r e a c h p r o f i l e i s i g n o r e d . )
C l i c k t h e " C o n f i g u r e V L A N " b u t t o n t o c o n f i g u r e t h e I D s u s e d b y
e a c h V L A N .
S e c u r i t y P r o f i l e S c r e e n
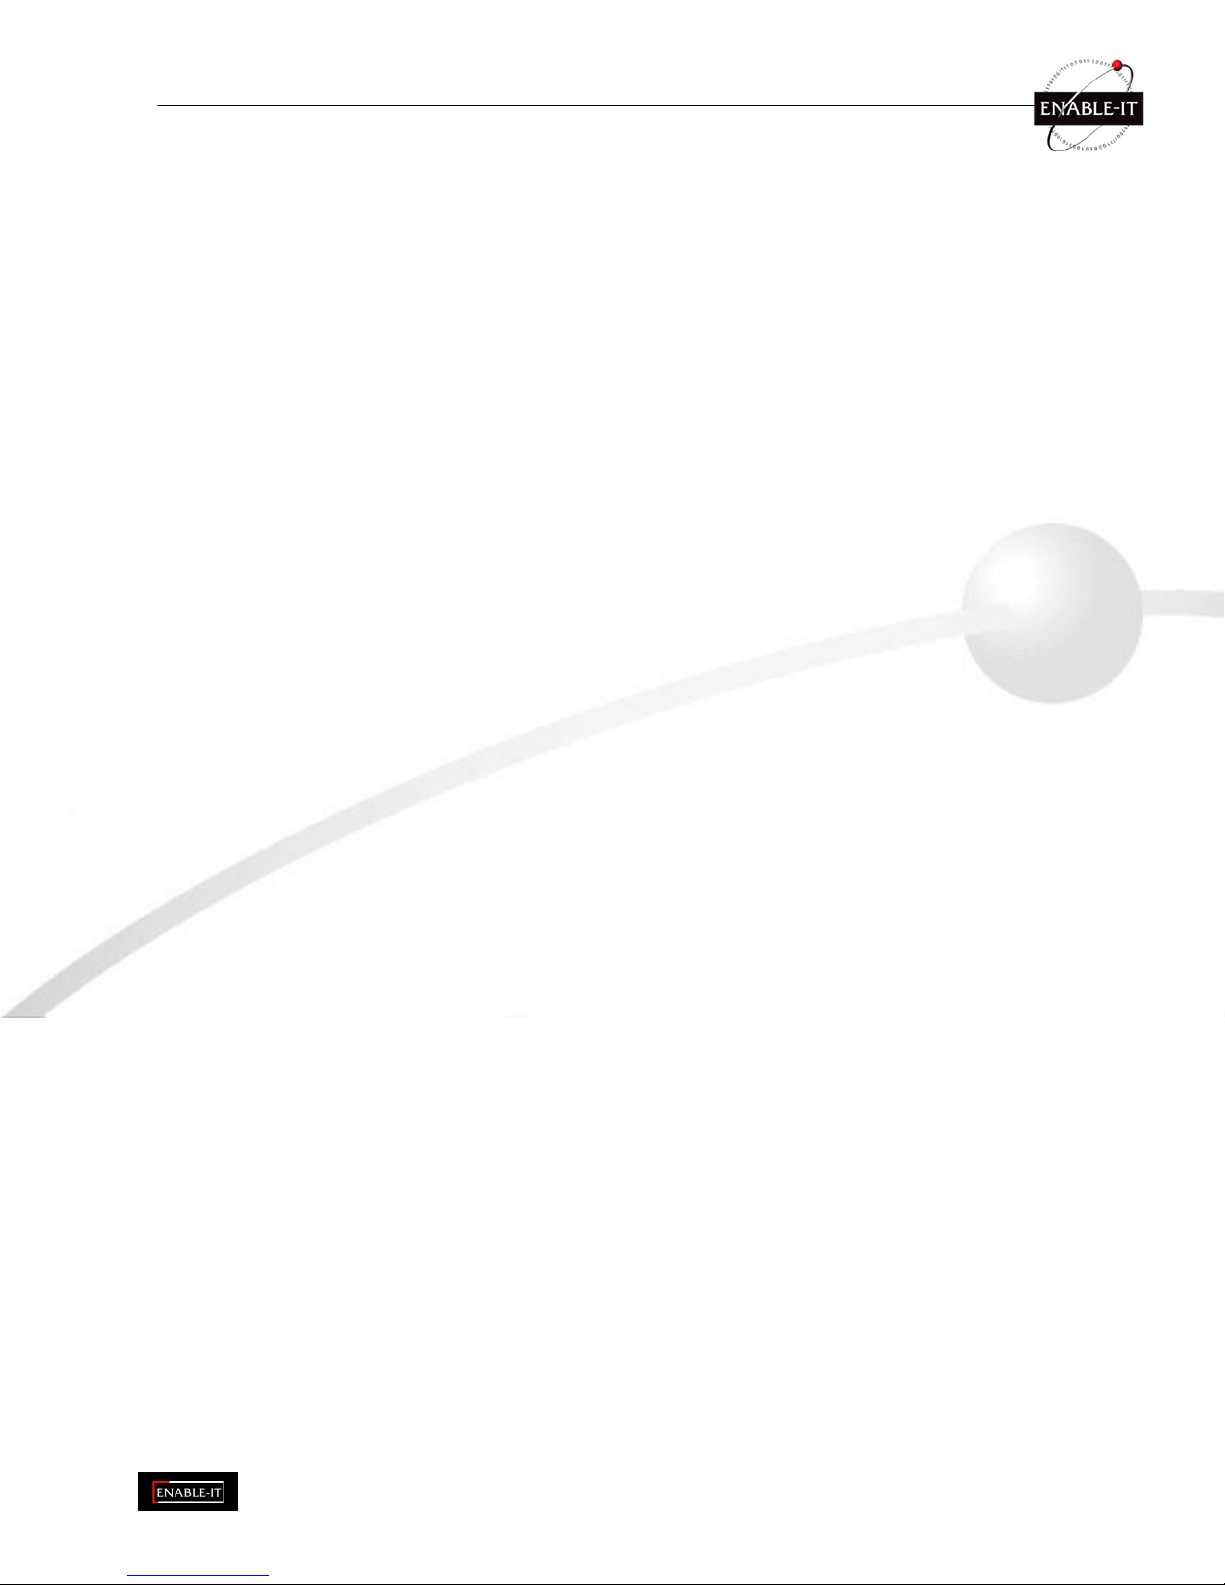
T h i s s c r e e n i s d i s p l a y e d w h e n y o u s e l e c t a P r o f i l e o n t h e S e c u r i t y P r o f i l e s s c r e e n , a n d c l i c k t h e C o n f i g u r e b u t t o n .
Figure 9: Security Profile Screen
P r o f i l e D a t a
E n t e r t h e d e s i r e d s e t t i n g s f o r e a c h o f t h e f o l l o w i n g :
P r o f i l e N a m e
E n t e r a s u i t a b l e n a m e f o r t h i s p r o f i l e .
S S I D
E n t e r t h e d e s i r e d S S I D . E a c h p r o f i l e m u s t h a v e a u n i q u e S S I D .
W i r e l e s s B a n d
S e l e c t t h e w i r e l e s s b a n d o r b a n d s f o r t h i s p r o f i l e . I f y o u r W i r e l e s s
A c c e s s P o i n t o n l y h a s a s i n g l e b a n d , t h e n o n l y 1 o p t i o n i s
a v a i l a b l e .
Page 16
P a g e 1 6 o f
9 3
S e c u r i t y S e t t i n g s
S e l e c t t h e d e s i r e d o p t i o n , a n d t h e n e n t e r t h e s e t t i n g s f o r t h e s e l e c t e d m e t h o d .
T h e a v a i l a b l e o p t i o n s a r e :
• None - No security is used. Anyone using the correct SSID can connect to your network.
• WEP - The 802.11b standard. Data is encrypted before transmission, but the encryption system is not very
strong.
• WPA-PSK - Like WEP, data is encrypted before transmission. WPA is more secure than WEP, and should be
used if possible. The PSK (Pre-shared Key) must be entered on each Wireless station. The 256Bit encryption
key is derived from the PSK, and changes frequently.
• WPA-802.1x - This version of WPA requires a Radius Server on your LAN to provide the client authentication
according to the 802.1x standard. Data transmissions are encrypted using the WPA standard.
If this option is selected:
• This Access Point must have a "client login" on the Radius Server.
• Each user must have a "user login" on the Radius Server.
• Each user's wireless client must support 802.1x and provide the login data when required.
• All data transmission is encrypted using the WPA standard. Keys are automatically generated, so no key
input is required.
• 802.1x - This uses the 802.1x standard for client authentication, and WEP for data encryption. If possible, you
should use WPA-802.1x instead, because WPA encryption is much stronger than WEP encryption.
If this option is selected:
• This Access Point must have a "client login" on the Radius Server.
• Each user must have a "user login" on the Radius Server.
• Each user's wireless client must support 802.1x and provide the login data when required.
• All data transmission is encrypted using the WEP standard. You only have to select the WEP key size;
the WEP key is automatically generated.
Page 17
P a g e 1 7 o f
9 3
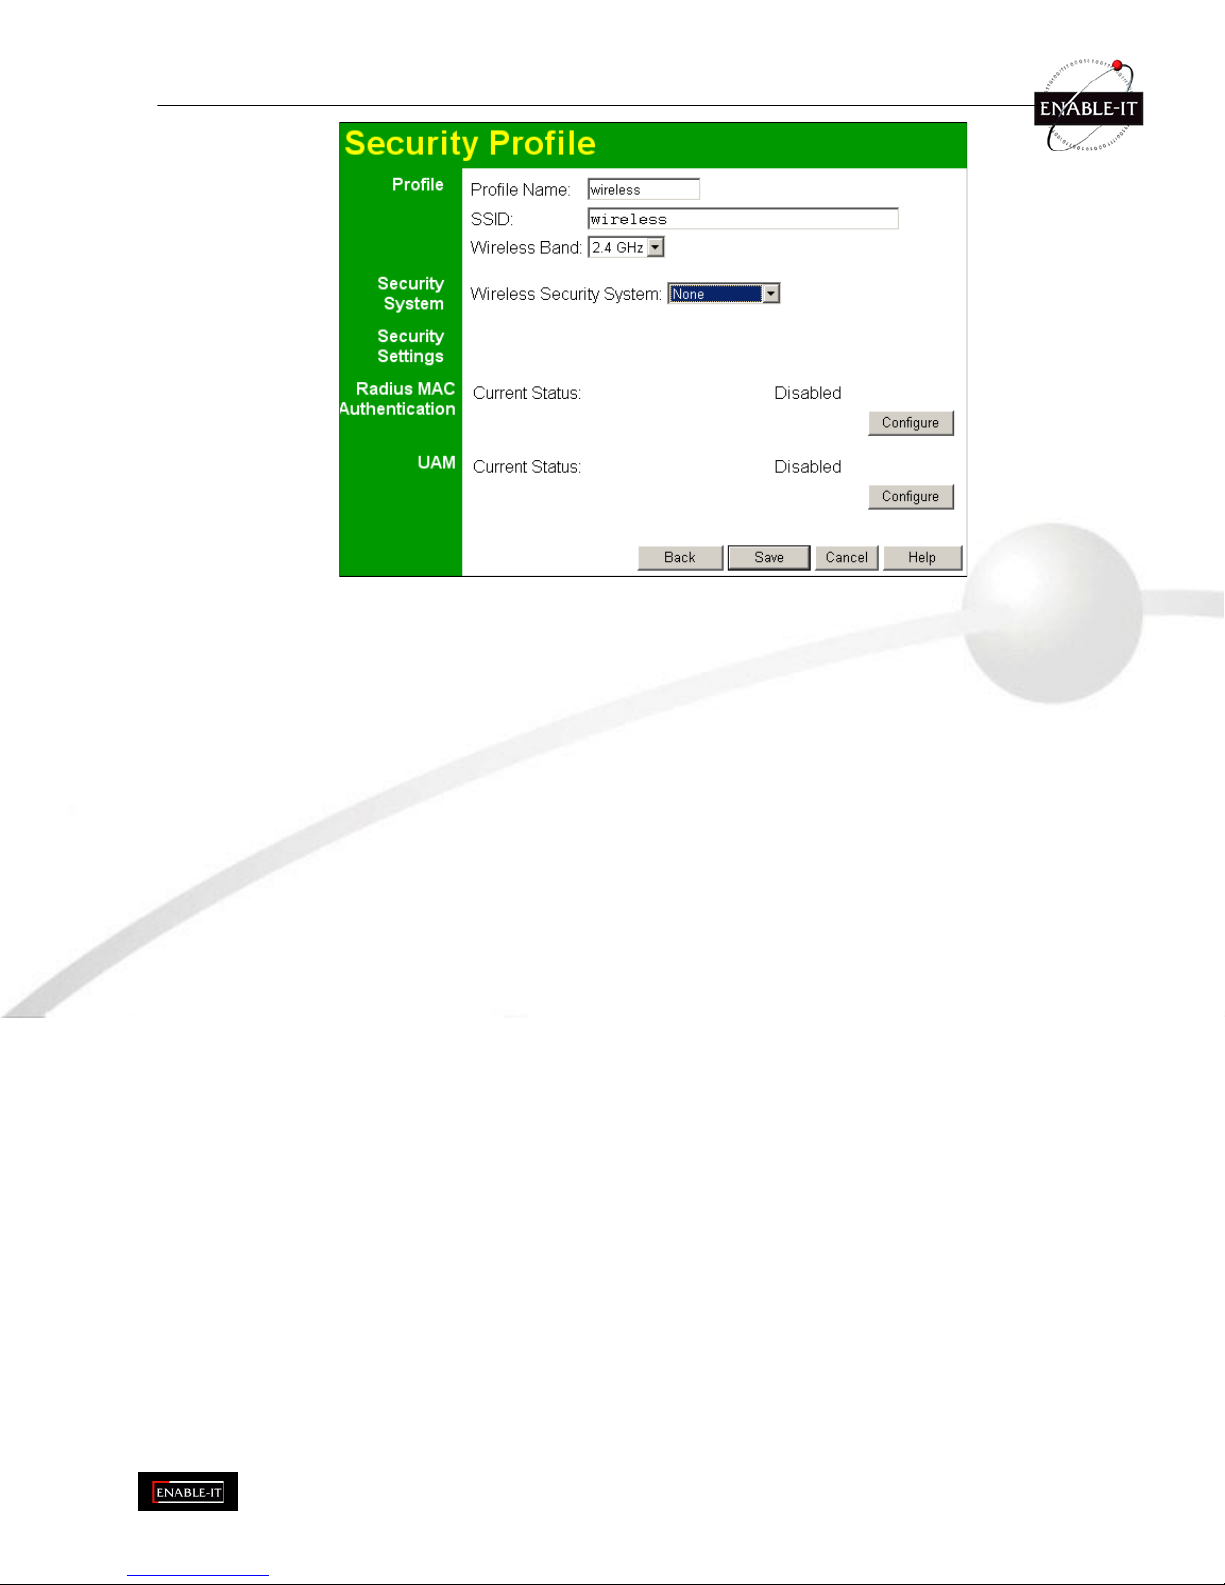
S e c u r i t y S e t t i n g s - N o n e
Figure 10: Wireless Security - None
N o s e c u r i t y i s u s e d . A n y o n e u s i n g t h e c o r r e c t S S I D c a n c o n n e c t t o y o u r n e t w o r k .
T h e o n l y s e t t i n g s a v a i l a b l e f r o m t h i s s c r e e n a r e R a d i u s M A C A u t h e n t i c a t i o n a n d U A M ( U n i v e r s a l A c c e s s M e t h o d ) .
R a d i u s M A C A u t h e n t i c a t i o n
R a d i u s M A C A u t h e n t i c a t i o n p r o v i d e s f o r M A C a d d r e s s c h e c k i n g w h i c h i s c e n t r a l i z e d o n y o u r R a d i u s s e r v e r . I f y o u d o n ' t
h a v e a R a d i u s S e r v e r , y o u c a n n o t u s e t h i s f e a t u r e .
Using MAC authentication
28. Ensure the Wireless Access Point can login to your Radius Server.
• Add a RADIUS client on the RADIUS server, using the IP address or name of the Wireless Access Point,
and the same shared key as entered on the Wireless Access Point.
• Ensure the Wireless Access Point has the correct address, port number, and shared key for login to your
Radius Server. These parameters are entered either on the Security page, or the Radius-based MAC
authentication sub-screen, depending on the security method used.
• On the Access Point, enable the Radius-based MAC authentication feature on the screen below.
29. Add Users on the Radius server as required. The username must be the MAC address of the Wireless client
you wish to allow, and the password must be blank.
30. When clients try to associate with the Access Point, their MAC address is passed to the Radius Server for
authentication.
• If successful, “
xx:xx:xx:xx:xx:xx MAC authentication
” is entered in the log, and client station status would
show as “authenticated” on the station list table;
• If not successful, “
xx:xx:xx:xx:xx:xx MAC authentication failed
” is entered in the log,, and station status is
shown as “authenticating” on the station list table.
Page 18
P a g e 1 8 o f
9 3
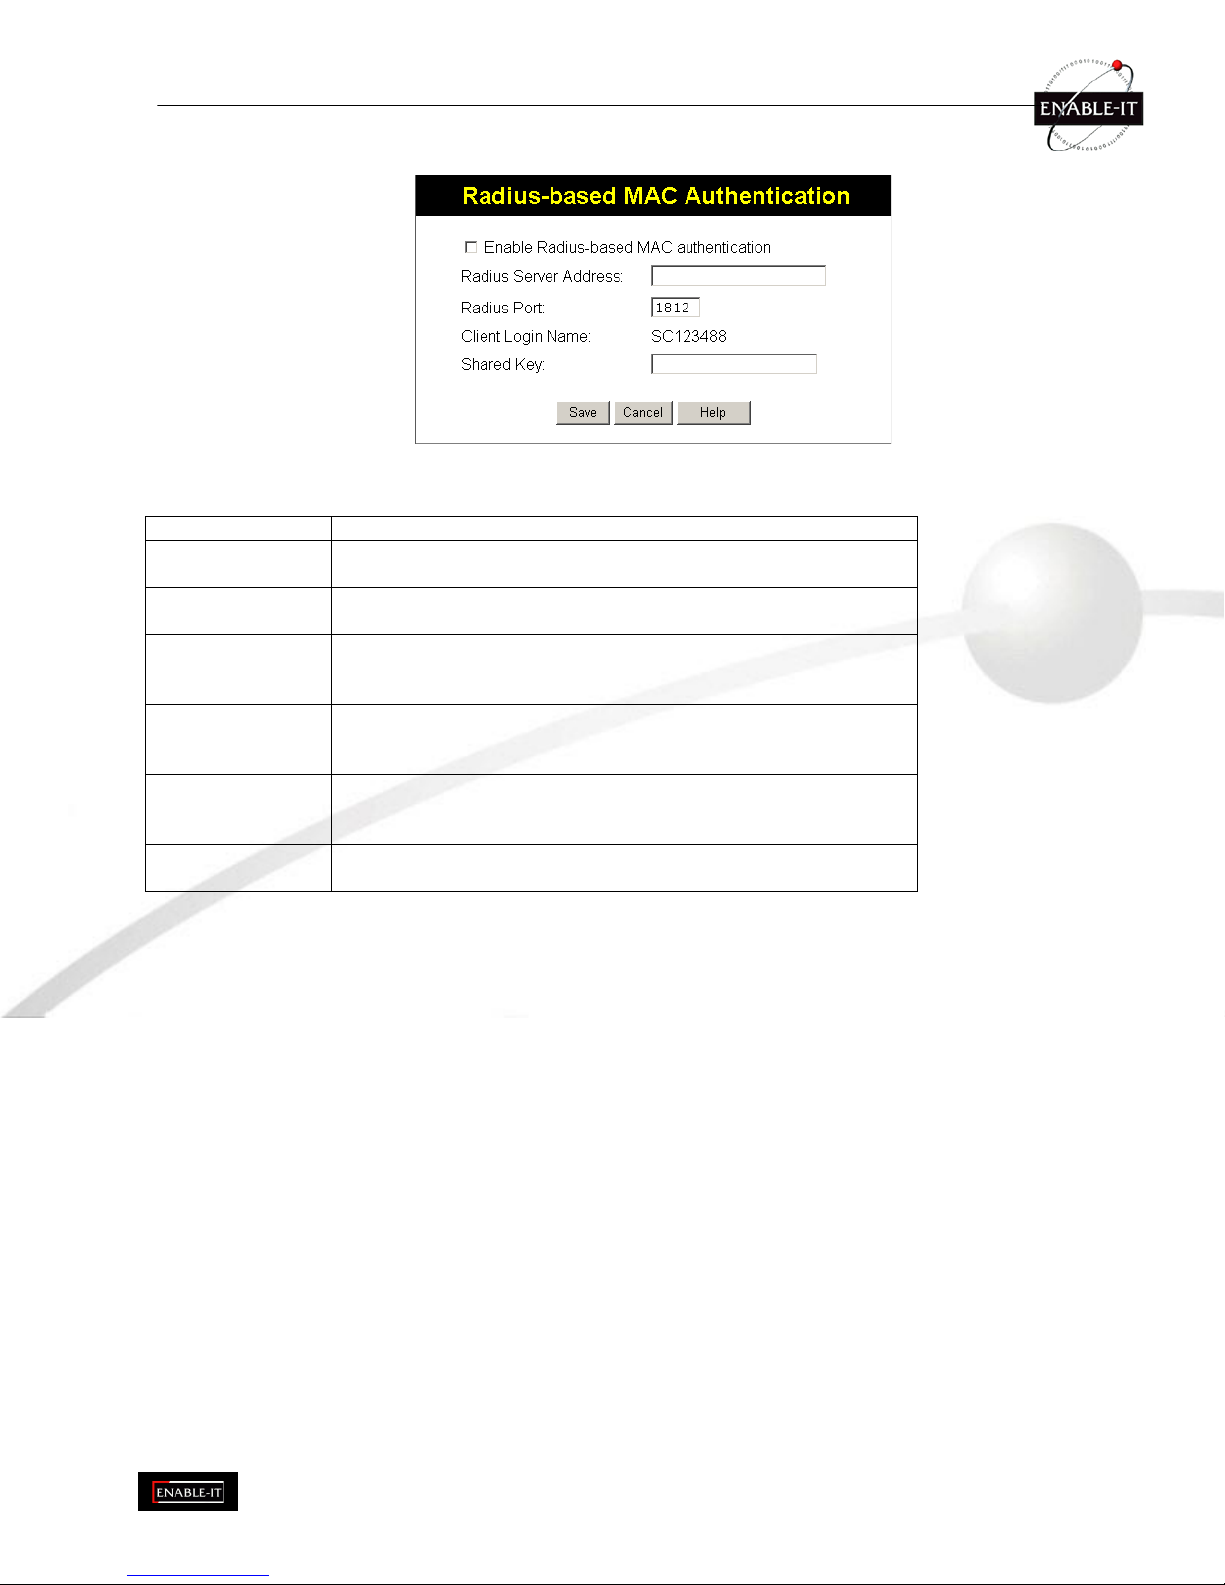
Radius-based MAC authentication Screen
T h i s s c r e e n w i l l l o o k d i f f e r e n t d e p e n d i n g o n t h e c u r r e n t s e c u r i t y s e t t i n g . I f y o u h a v e a l r e a d y p r o v i d e d t h e a d d r e s s o f y o u r
R a d i u s s e r v e r , y o u w o n ' t b e p r o m p t e d f o r i t a g a i n . O t h e r w i s e , y o u m u s t e n t e r t h e d e t a i l s o f y o u r R a d i u s S e r v e r o n t h i s
s c r e e n .
Figure 11: Radius-based MAC Authentication Screen
D a t a - R a d i u s -b a s e d M A C A u t h e n t i c a t i o n S c r e e n
En a b l e . . .
E n a b l e t h i s i f y o u w i s h t o R a d i u s -b a s e d M A C a u t h e n t i c a t i o n .
R a d i u s S e r v e r
A d d r e s s
I f t h i s f i e l d i s v i s i b l e , e n t e r t h e n a m e o r I P a d d r e s s o f t h e R ad i u s
S e r v e r o n y o u r n e tw o r k .
R a d i u s P o r t
I f t h i s f i e l d i s v i s i b l e , e n t e r t h e p o r t n u m b e r u s e d f o r c o n n e ct i o n s t o
t h e R a d i u s S e r v e r .
C l i e n t L o g i n
N a m e
I f t h i s f i e l d i s v i s i b l e , i t d i s p l a y s t h e n a m e u s e d f o r t h e C l i e n t L o g i n
o n t h e R a d i u s S e r v e r . T h i s L o g i n n a m e m u s t b e c r e a t e d o n t h e
R a d i u s S e r v e r .
S h a r e d K e y
I f t h i s f i e l d i s v i s i b l e , i t i s u s e d f o r t h e C l i e n t L o g i n o n t h e R ad i u s
S e r v e r . E n t e r t h e k e y v a l u e t o m a t c h t h e v a l u e o n t h e R a d i u s
S e r v e r .
W E P K e y
I f t h i s f i e l d i s v i s i b l e , i t i s f o r t h e W E P k e y u s e d t o e n c r y p t d a t a
t r a n s m i ss i o n s t o t h e R a d i u s S e r v e r . E n t e r t h e d e s i r e d k e y v a l u e i n
H E X , a n d e n s u r e t h e R a d i u s S e r v e r h a s t h e s a m e v a l u e .
W E P K e y I n d e x
I f t h i s f i e l d i s v i s i b l e , s e l e c t t h e d e s i r e d k e y i n d e x . A n y v a l u e c a n b e
u s e d , p r o v i d e d i t m a t c h e s t h e v a l u e o n t h e R a d i u s S e r v e r .
Page 19
P a g e 1 9 o f
9 3
U A M
U A M ( U n i v e r s a l A c c e s s M e t h o d ) i s i n t e n d e d f o r u s e i n I n t e r n e t c a f e s , H o t S p o t s , a n d o t h e r s i t e s w h e r e t h e A c c e s s P o i n t
i s u s e d t o p r o v i d e I n t e r n e t A c c e s s .
I f e n a b l e d , t h e n H T T P ( T C P , p o r t 8 0 ) c o n n e c t i o n s a r e c h e c k e d . ( U A M o n l y w o r k s o n H T T P c o n n e c t i o n s ; a l l o t h e r t r a f f i c
i s i g n o r e d . ) I f t h e u s e r h a s n o t b e e n a u t h e n t i c a t e d , I n t e r n e t a c c e s s i s b l o c k e d , a n d t h e u s e r i s r e -d i r e c t e d t o a n o t h e r w e b
p a g e . T y p i c a l l y , t h i s w e b p a g e i s o n y o u r W e b s e r v e r , a n d e x p l a i n s h o w t o p a y f o r a n d o b t a i n I n t e r n e t a c c e s s .
T o u s e U A M , y o u n e e d a R a d i u s S e r v e r f o r A u t h e n t i c a t i o n . T h e " R a d i u s S e r v e r S e t u p " m u s t b e c o mp l e t e d b e f o r e y o u
c a n u s e U A M . T h e r e q u i r e d s e t u p d e p e n d s o n w h e t h e r y o u a r e u s i n g “ I n t e r n a l ” o r “ E x t e r n a l ” a u t h e n t i c a t i o n .
• Internal authentication uses the web page built into the Wireless Access Point.
• External authentication uses a web page on your Web server. Generally, you should use External
authentication, as this allows you to provide relevant and helpful information to users.
UAM authentication - Internal
31. Ensure the Wireless Access Point can login to your Radius Server.
• Add a RADIUS client on RADIUS server, using the IP address or name of the Wireless Access Point, and
the same shared key as entered on the Wireless Access Point.
• Ensure the Wireless Access Point has the correct address, port number, and shared key for login to your
Radius Server. These parameters are entered either on the Security page, or the UAM sub-screen,
depending on the security method used.
32. Add users on your RADIUS server as required, and allow access by these users.
33. Client PCs must have the correct Wireless settings in order to associate with the Wireles Access Point.
34. When an associated client tries to use HTTP (TCP, port 80) connections, they will be re-directed to a user
login page.
35. The client (user) must then enter the user name and password, as defined on the Radius Server. (You must
provide some system to let users know the correct name and password to use.)
36. If the user name and password is correct, Internet access is allowed.
Otherwise, the user remains on the login page.
• Clients which pass the authentication are listed as “
xx:xx:xx:xx:xx:xx WEB authentication
” in the log table,
and station status would show as “Authenticated” on the station list table.
• If a client fails authentication, “
xx:xx:xx:xx:xx:xx WEB authentication failed
” shown in the log, and station
status is shown as “Authenticating” on the station list table.
UAM authentication - External
37. Ensure the Wireless Access Point can login to your Radius Server.
• Add a RADIUS client on RADIUS server, using the IP address or name of the Wireless Access Point, and
the same shared key as entered on the Wireless Access Point.
• Ensure the Wireless Access Point has the correct address, port number, and shared key for login to your
Radius Server. These parameters are entered either on the Security page, or the UAM sub-screen,
depending on the security method used.
38. On your Web Server, create a suitable welcome page.
The welcome page must have a link or button to allow the user to input their user name and password
on the uamlogon.htm page on the Access Point.
39. On the Access Point’s UAM screen, select External Web-based Authentication, and enter the URL for the
welcome page on your Web server.
40. Add users on your RADIUS server as required, and allow access by these users.
41. Client PCs must have the correct Wireless settings in order to associate with the Wireless Access Point.
42. When an associated client tries to use HTTP (TCP, port 80) connections, they will be re-directed to the
welcome page on your Web Server. They must then click the link or button in order to reach the Access
Point’s login page.
43. The client (user) must then enter the user name and password, as defined on the Radius Server. (You must
provide some system to let users know the correct name and password to use.)
44. If the user name and password is correct, Internet access is allowed.
Otherwise, the user remains on the login page.
Page 20
P a g e 2 0 o f
9 3
• Clients which pass the authentication are listed as “
xx:xx:xx:xx:xx:xx WEB authentication
” in the log table,
and station status would show as “Authenticated” on the station list table.
• If a client fails authentication, “
xx:xx:xx:xx:xx:xx WEB authentication failed
” is shown in the log, and station
status is shown as “Authenticating” on the station list table.
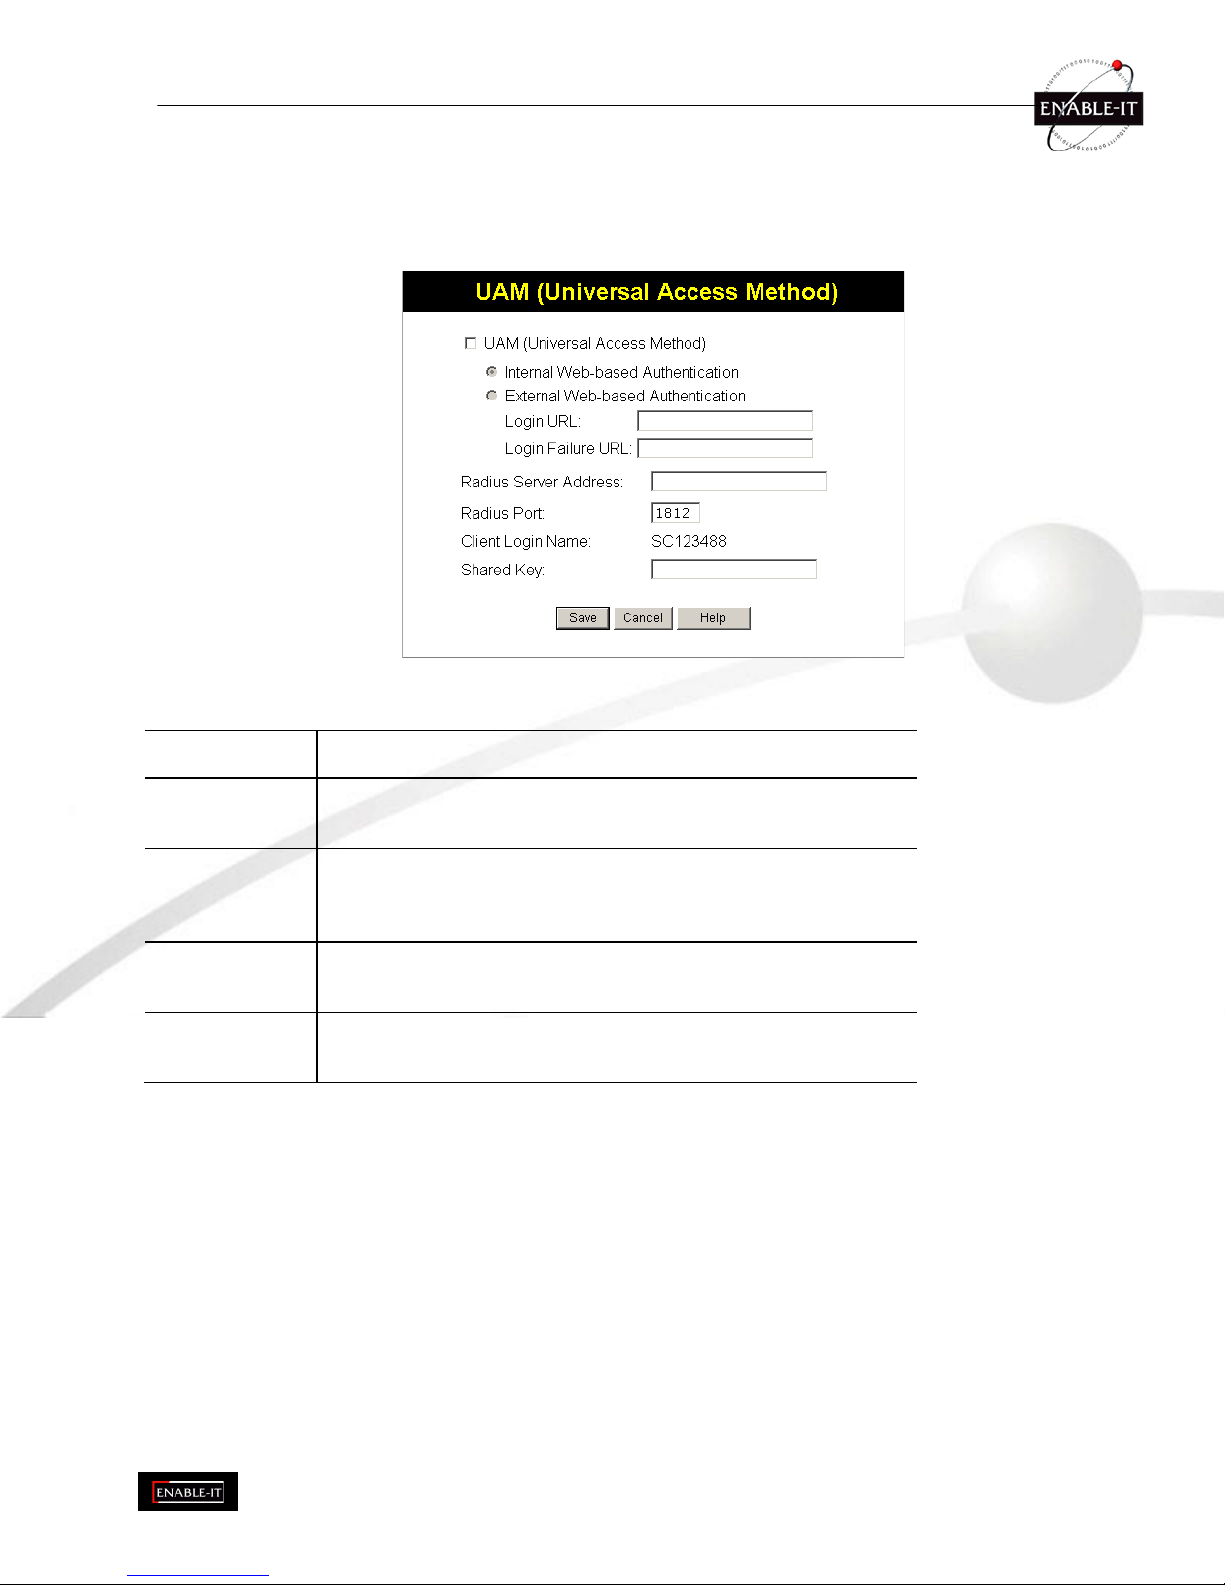
UAM Screen
T h e U A M s c r e e n w i l l l o o k d i f f e r e n t d e p e n d i n g o n t h e c u r r e n t s e c u r i t y s e t t i n g . I f y o u h a v e a l r e a d y p r o v i d e d t h e a d d r e s s o f
y o u r R a d i u s s e r v e r , y o u w o n ' t b e p r o m p t e d f o r i t a g a i n .
Figure 12: UAM Screen
D a t a - U A M S c r e e n
E n a b l e
E n a b l e t h i s i f y o u w i s h t o u s e t h i s f e a t u r e . S e e t h e s e c t i o n a b o v e f o r
d e t a i l s o f u s i n g U A M .
I n t e r n a l
W e b -b a s e d
A u t h e n t i c at i o n
I f s e l e c t e d , t h e n w h e n a u s e r f i r s t t r i e s t o a c c e s s t h e I n t e r n e t , t h e y
w i l l b e b l o c k e d , a n d r e -d i r e c t e d t o t h e b u i l t -i n l o g i n p a g e . T h e l o g o n
d a t a i s t h e n s e n t t o t h e R a d i u s S e r v e r f o r a u t h e n t i c at i o n .
E x t e r n a l
W e b -b a s e d
A u t h e n t i c at i o n
I f s e l e c t e d , t h e n w h e n a u s e r f i r s t t r i e s t o a c c e s s t h e I n t e r n e t , t h e y
w i l l b e b l o c k e d , a n d r e -d i r e c t e d t o t h e U R L b e l o w . T h i s n e e d s t o b e
o n y o u r o w n l o c a l W e b S e r v e r . T h e p a g e m u s t a l s o l i n k b a c k t o t h e
b u i l t -i n l o g i n p a g e o n t h i s d e v i c e t o c o m p l e t e t h e l o g i n p r o c e d u r e .
L o g i n U R L
E n t e r t h e U R L o f t h e p a g e o n y o u r l o c a l W e b S e r v e r y o u w i s h u s e r s
t o s e e w h e n t h e y a t t e m p t t o a c c e s s t h e I n t e r n e t , b u t a r e n o t l o g g e d
i n .
L o g i n F a i l u r e
U R L
E n t e r t h e U R L o f t h e p a g e o n y o u r l o c a l W e b S e r v e r y o u w i s h u s e r s
t o s e e i f t h e i r l o g i n f a i l s . ( T h i s m a y b e t h e s a m e U R L a s t h e L o g i n
U R L ) .
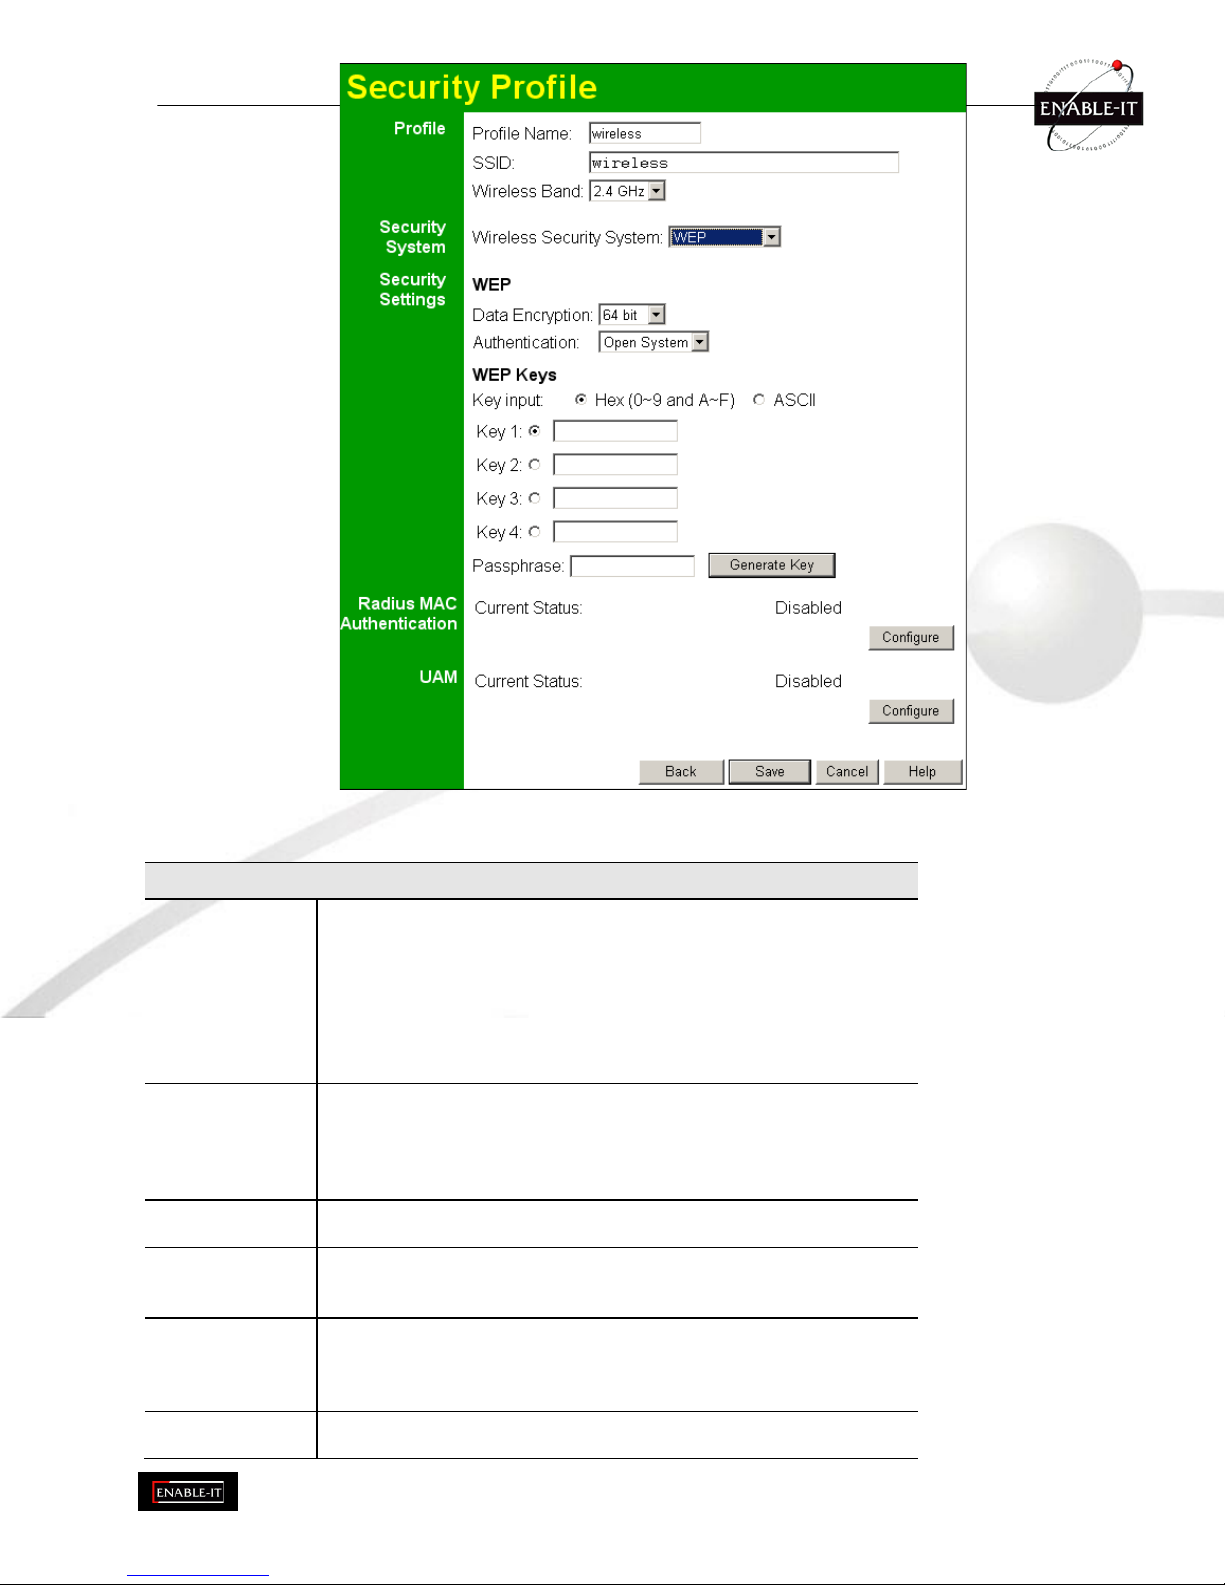
S e c u r i t y S e t t i n g s - W E P
T h i s i s t h e 8 0 2 . 1 1 b s t a n d a r d . D a t a i s e n c r y p t e d b e f o r e t r a n s m i s s i o n , b u t t h e e n c r y pt i o n s y s t e m i s n o t v e r y s t r o n g .
Page 21
P a g e 2 1 o f
9 3
Figure 13: WEP Wireless Security
D a t a - W E P S c r e e n
WEP
D a t a
E n c r y pt i o n
S e l e c t t h e d e s i r e d o p t i o n , a n d e n s u r e y o u r W i r e l e s s s t a t i o n s h a v e
t h e s a m e s e t t i n g :
• 64 Bit Encryption - Keys are 10 Hex (5 ASCII) characters.
• 128 Bit Encryption - Keys are 26 Hex (13 ASCII)
characters.
• 152 Bit Encryption - Keys are 32 Hex (16 ASCII)
characters.
A u t h e n t i c a t i o n
N o r m a l l y , y o u c a n l e a v e t h i s a t “ A u t o m a t i c ” , s o t h a t W i r e l e s s
S t a t i o n s c a n u s e e i t h e r m e t h o d ( " O p e n S y s t e m " o r " S h a r e d K e y " . ) .
I f y o u w i s h t o u s e a p a r t i c u l a r m e t h o d , s e l e c t t h e a p p r o p r i a t e v a l u e " O p e n S y s t e m " o r " S h a r e d K e y " . A l l W i r e l e s s s t a t i o n s m u s t t h e n b e
s e t t o u s e t h e s a m e m e t h o d .
K e y I n p u t
S e l e c t " H e x " o r " A S C I I " d e p e n d i n g o n y o u r i n p u t m e t h o d . ( A l l k e y s
a r e c o n v e r t e d t o H e x , A S C I I i n p u t i s o n l y f o r c o n v e ni e n c e . )
K e y V a l u e
E n t e r t h e k e y v a l u e s y o u w i s h t o u s e . T h e d e f a u l t k e y , s e l e c t e d b y
t h e r a d i o b u t t o n , i s r e q u i r e d . T h e o t h e r k e y s a r e o p t i o n a l . O t h e r
s t a t i o n s m u s t h a v e m a t c h i n g k e y v a l u e s .
P a s s p h r a s e
U s e t h i s t o g e n e r a t e a k e y o r k e y s , i n s t e a d o f e n t e r i n g t h e m d i r e c t l y .
E n t e r a w o r d o r g r o u p o f p r i n t a b l e c h a r a c t e r s i n t h e P a s s p h r a s e b o x
a n d c l i c k t h e " G e n e r a t e K e y " b u t t o n t o a u t om a t i c a l l y c o n f i g u r e t h e
W E P K e y ( s ) .
R a d i u s M A C
A u t h e n t ic a t i o n
T h e c u r r e n t s t a t u s i s d i s p l a y e d .
C l i c k t h e " C o n f i g u r e " b u t t o n t o c o n f i g u r e t h i s f e a t u r e i f r eq u i r e d .
Page 22
P a g e 2 2 o f
9 3
U A M
T h e c u r r e n t s t a t u s i s d i s p l a y e d .
C l i c k t h e " C o n f i g u r e " b u t t o n t o c o n f i g u r e t h i s f e a t u r e i f r eq u i r e d .
Page 23
P a g e 2 3 o f
9 3
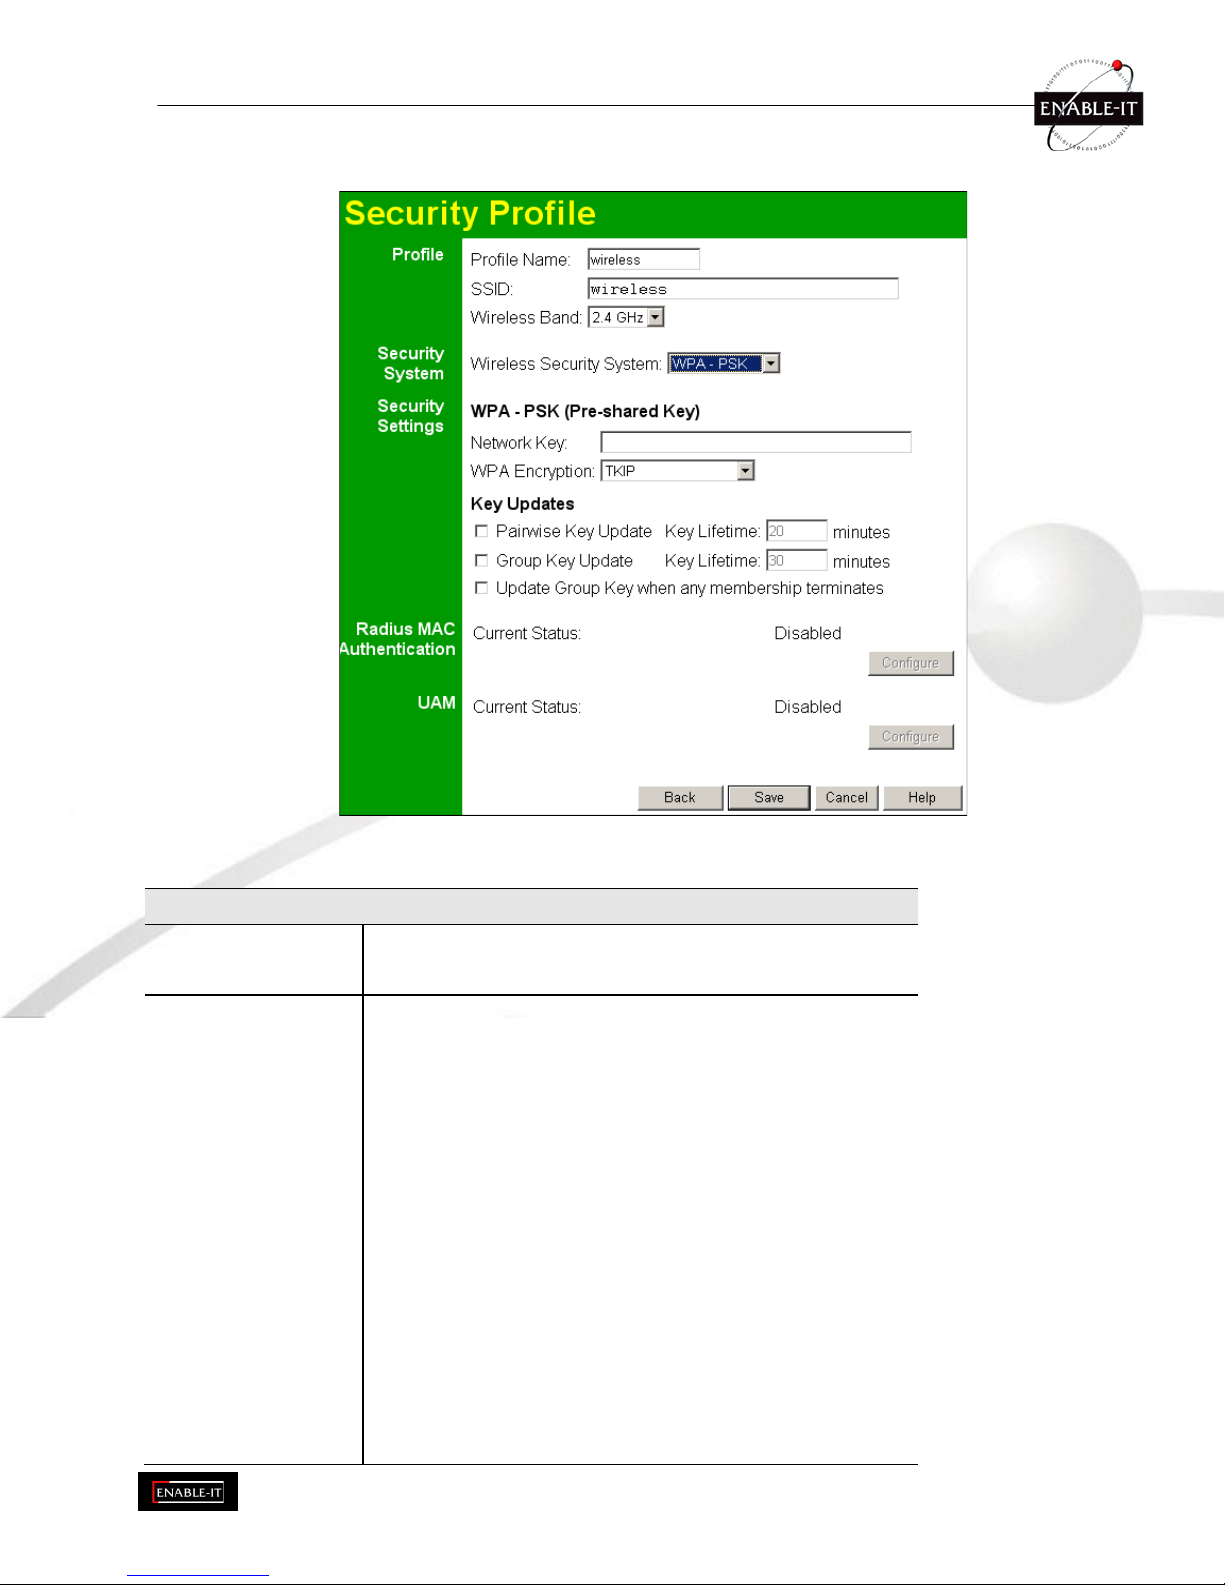
S e c u r i t y S e t t i n g s - W P A -P S K
L i k e W E P , d a t a i s e n c r y p t e d b e f o r e t r a n s m i s s i o n . W P A i s m o r e s e c u r e t h a n W E P , a n d s h o u l d b e u s e d i f p o s s i b l e . T h e
P S K ( P r e -s h a r e d K e y ) m u s t b e e n t e r e d o n e a c h W i r e l e s s s t a t i o n . T h e 2 5 6 B i t e n c r y p t i o n k e y i s d e r i v e d f r o m t h e P S K ,
a n d c h a n g e s f r e q u e n t l y .
Figure 14: WPA-PSK Wireless Security
D a t a - W P A -P S K S c r e e n
WPA-PSK
N e t w o r k K e y
E n t e r t h e k e y v a l u e . D a t a i s e n c r y p t e d u s i n g a 2 5 6 B i t k e y
d e r i v e d f r o m t h i s k e y . O t h e r W i r e l e s s S t a t i o n s m u s t u s e t h e
s a m e k e y .
W P A E n c r y p t i o n
S e l e c t t h e d e s i r e d o p t i o n . O t h e r W i r e l e s s S t a t i o n s m u s t u s e
t h e s a m e m e t h o d .
• TKIP - Unicast (point-to-point) transmissions are
encrypted using TKIP, and multicast (broadcast)
transmissions are not encrypted.
• TKIP + 64 bit WEP - Unicast (point-to-point)
transmissions are encrypted using TKIP, and multicast
(broadcast) transmissions are encrypted using 64 bit
WEP.
• TKIP + 128 bit WEP - Unicast (point-to-point)
transmissions are encrypted using TKIP, and multicast
(broadcast) transmissions are encrypted using 128 bit
WEP.
• AES - CCMP - CCMP is the most common sub-type of
AES (Advanced Encryption System). Most systems will
simply say "AES". If selected, both Unicast (point-topoint) and multicast (broadcast) transmissions are
encrypted using AES.
• AES - TKIP - If selected, Unicast (point-to-point) uses
Page 24
P a g e 2 4 o f
9 3
AES-CCMP and multicast (broadcast) transmissions
are encrypted using TKIP.
P a i r w i s e K e y U pd a t e
T h i s r e f e r s t o t h e k e y u s e d f o r p o i n t -t o -p o i n t t r a n s m i s s i o n s .
E n a b l e t h i s i f y o u w a n t t h e k e y s t o b e u p d a t e d r e g u l a r l y .
K e y L i f e t i m e
T h i s f i e l d d e t e r m i n e s h o w o f t e n P a i r w i s e k e y s a r e d y n a m ic a l l y
u p d a t e d . E n t e r t h e d e s i r e d v a l u e .
G r o u p K e y U p d a t e
T h i s r e f e r s t o t h e k e y u s e d f o r b r o a d c a s t t r a n s m i s s i o n s . E n a b l e
t h i s i f y o u w a n t t h e k e y s t o b e u p d a t e d r e g u l a r l y .
K e y L i f e t i m e
T h i s f i e l d d e t e r m i n e s h o w o f t e n t h e G r o u p k e y i s d y n a m ic a l l y
u p d a t e d . E n t e r t h e d e s i r e d v a l u e .
U p d a t e G r o u p k e y
w h e n a n y
m e m b e rs h i p
t e r m in a t e s
I f e n a b l e d , t h e G r o u p k e y w i l l b e u p d a t e d w h e n e v e r a n y
m e mb e r l e a v e s t h e g r o u p o r d i s a s s o c i a t e s f r o m t h e A c c e s s
P o i n t .
R a d i u s M A C
A u t h e n t ic a t i o n
T h e c u r r e n t s t a t u s i s d i s p l a y e d . T h i s w i l l a l w a y s b e " D i sa b l e d " ,
b e c a u s e R a d i u s M A C A u t h e n t i c a t i o n i s n o t a v a i l a b l e w i t h
W P A -P S K . T h e C o n f i g u r e b u t t o n f o r t h i s f e a t u r e w i l l a l s o b e
d i s a b l e d .
U A M
T h e c u r r e n t s t a t u s i s d i s p l a y e d . T h i s w i l l a l w a y s b e " D i sa b l e d " ,
b e c a u s e U A M i s n o t a v a i l a b l e w i t h W P A -P S K . T h e C o n f i gu r e
b u t t o n f o r t h i s f e a t u r e w i l l a l s o b e d i s a b l e d .
Page 25
P a g e 2 5 o f
9 3
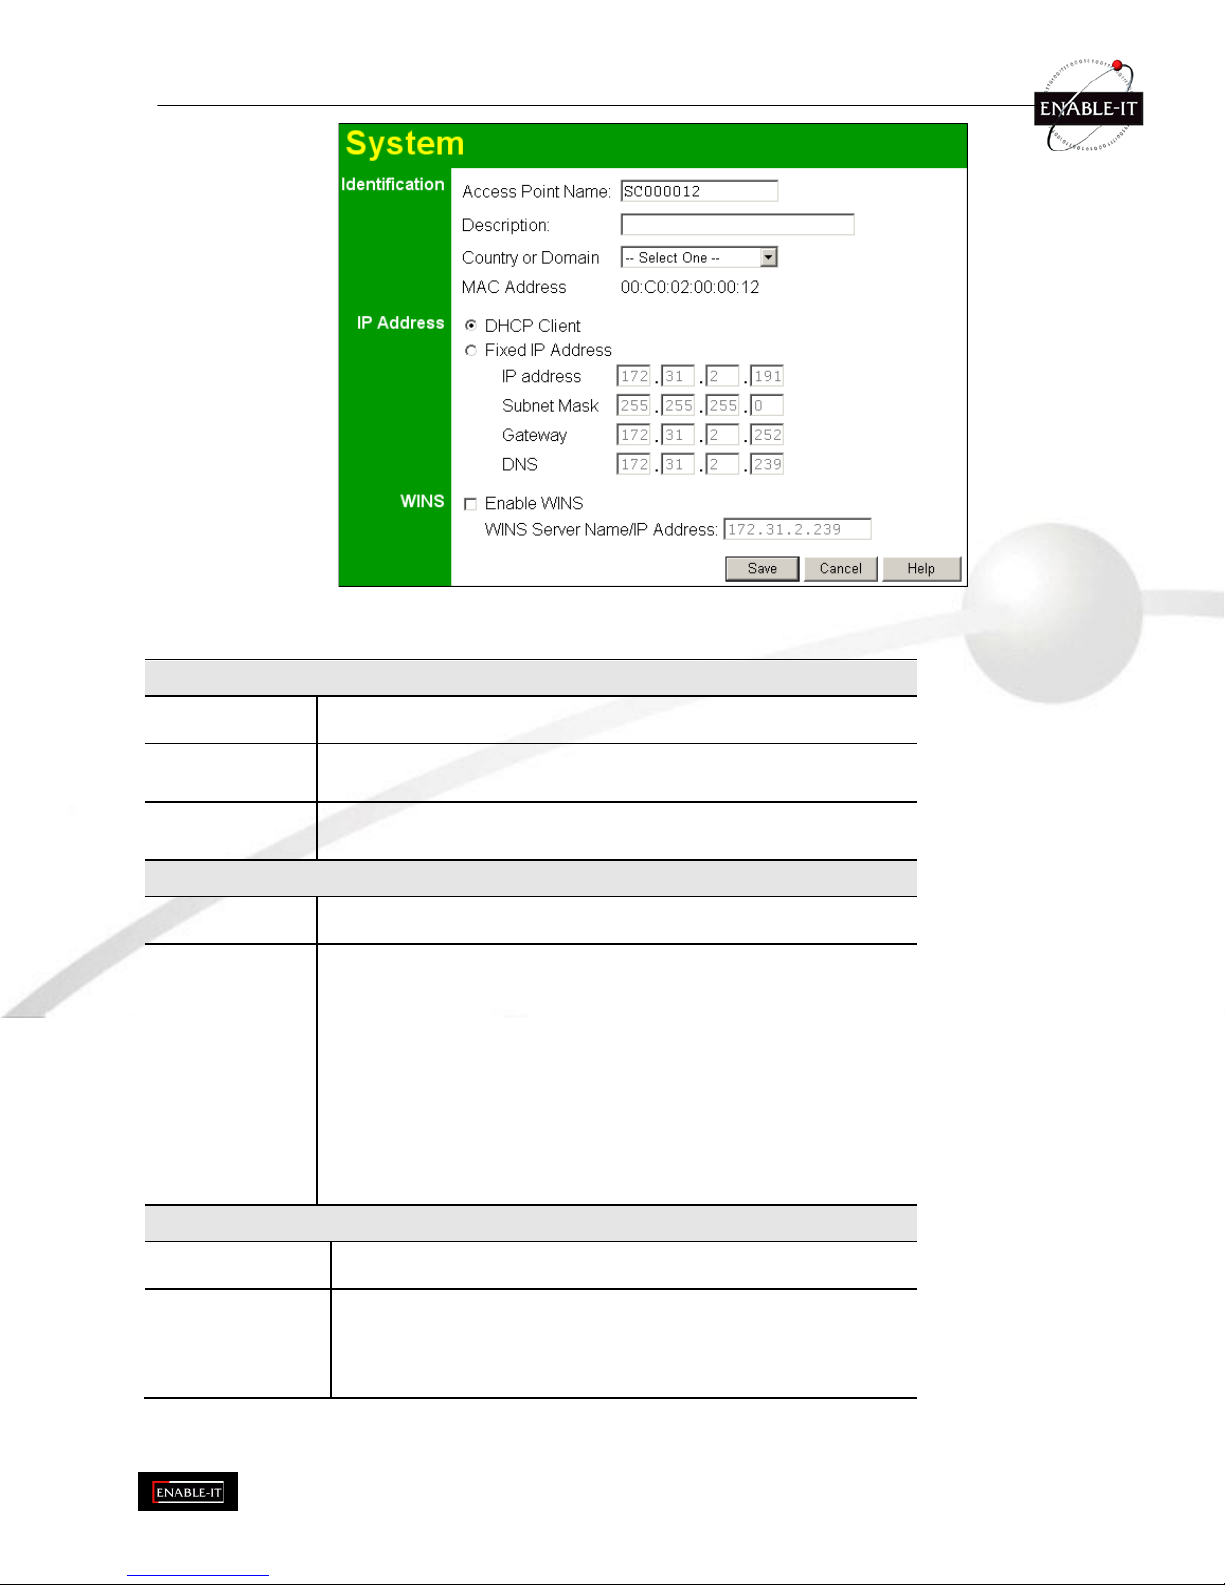
S y s t e m S c r e e n
C l i c k S y s t e m o n t h e m e n u t o v i e w a s c r e e n l i k e t h e f o l l o wi n g .
Figure 15: System Screen
D a t a - S y s t e m S c r e e n
Identification
A c c e s s P o i n t
N a m e
E n t e r a s u i t a b l e n a m e f o r t h i s A c c e s s P o i n t .
D e s c r i p
t i o n
I f d e s i r e d , y o u c a n e n t e r a d e s c r i p t i o n f o r t h e A c c e s s P o i n t .
C o u n t r y
Dom a i n
S e l e c t t h e c o u n t r y o r d o m a i n m a t c h i n g y o u r c u r r e n t l o c a t i o n .
IP Address
D H C P C l i e n t
S e l e c t t h i s o p t i o n i f y o u h a v e a D H C P S e r v e r o n y o u r L A N , a n d y o u
w i s h t h e A c c e s s P o i n t t o o b t a i n a n I P a d d r e s s a u t o m a t i c a l l y .
F i x e d
I f s e l e c t e d , t h e f o l l o w i n g d a t a m u s t b e e n t e r e d .
• IP Address - The IP Address of this device. Enter an
unused IP address from the address range on your LAN.
• Subnet Mask - The Network Mask associated with the IP
Address above. Enter the value used by other devices on
your LAN.
• Gateway - The IP Address of your Gateway or Router. Enter
the value used by other devices on your LAN.
• DNS - Enter the DNS (Domain Name Server) used by PCs
on your LAN.
WINS
E n a b l e W I N S
I f y o u r L A N h a s a W I N S s e r v e r , y o u c a n e n a b l e t h i s t o h a v e t h i s
A P r e g i s t e r w i t h t h e W I N S s e r v e r .
W I N S
S e r v e r
N a m e / I P
Add r e s s
E n t e r t h e n a m e o r I P a d d r e s s o f y o u r W I N S s e r v e r .
Page 26
P a g e 2 6 o f
9 3
W i r e l e s s S c r e e n s
T h e r e a r e t w o ( 2 ) c o n f i g u r a t i o n s c r e e n s a v a i l a b l e :
• Basic Settings
• Advanced
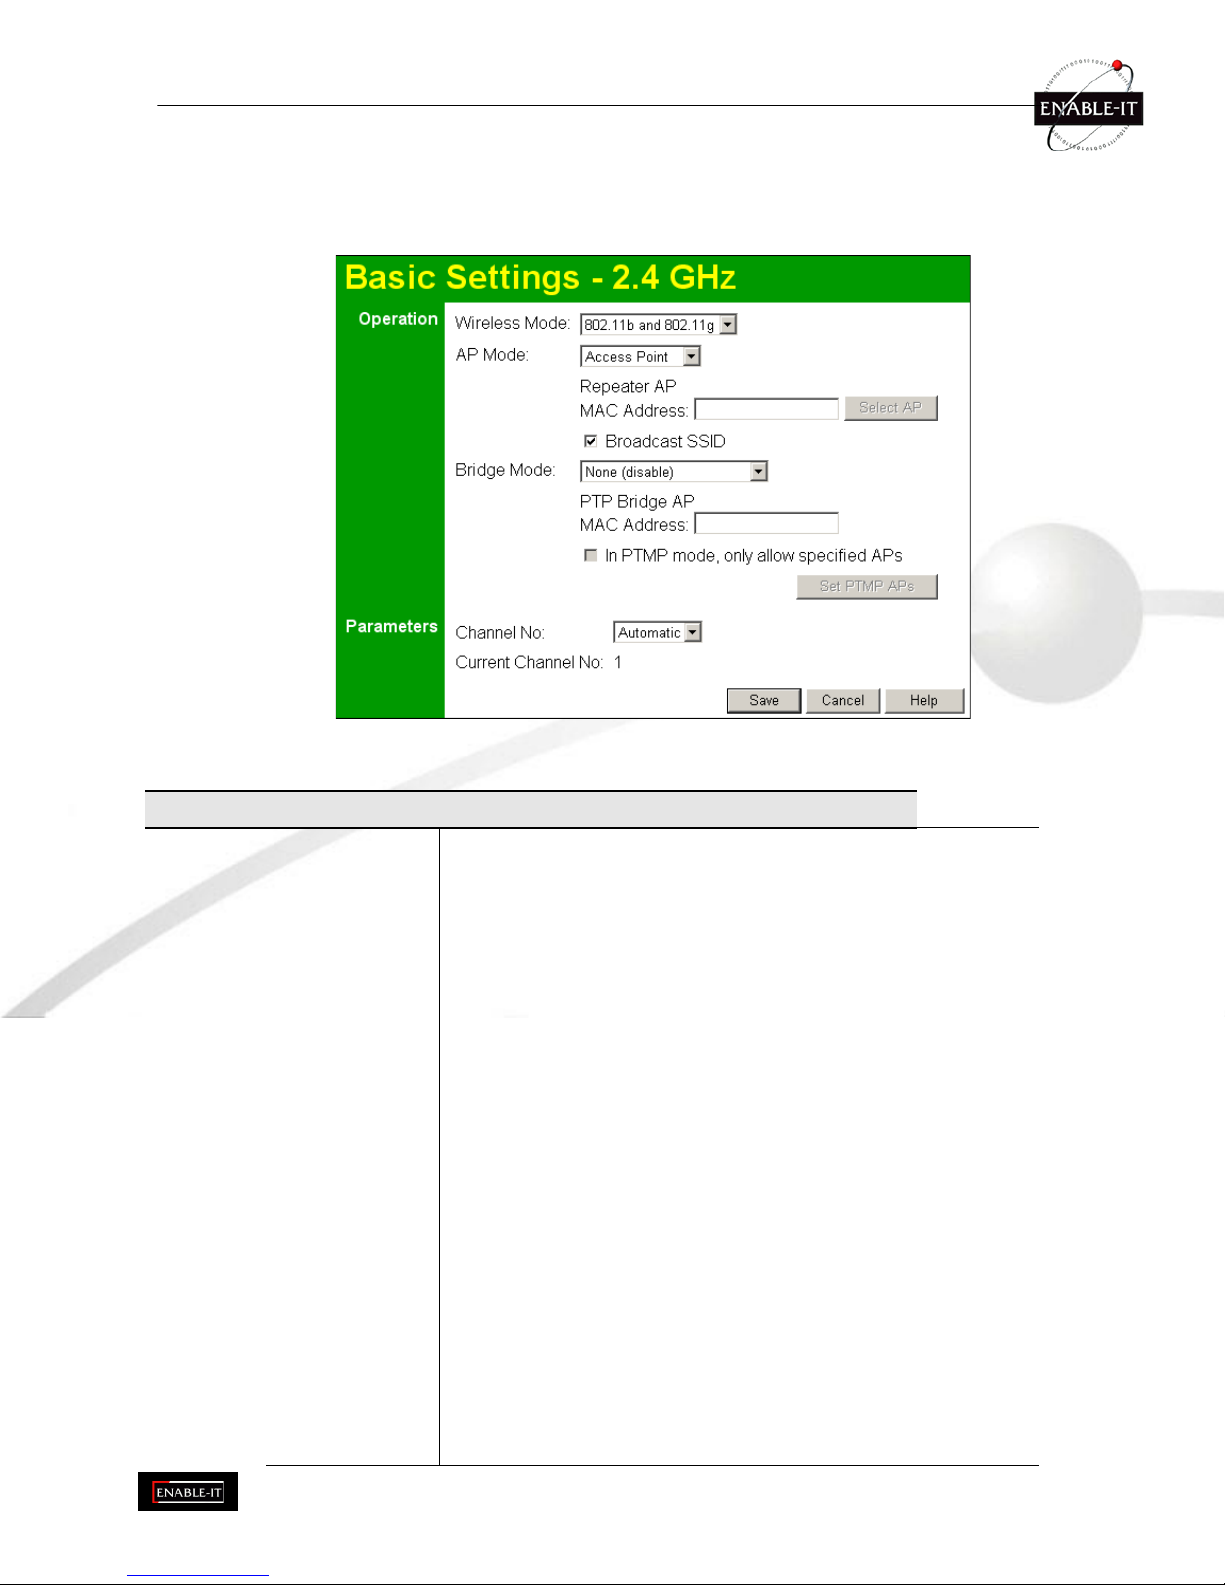
B a s i c S e t t i n g s S c r e e n
T h e s e t t i n g s o n t h i s s c r e e n m u s t m a t c h t h e s e t t i n g s u s e d b y W i r e l e s s S t a t i o n s .
C l i c k B a s i c o n t h e m e n u t o v i e w a s c r e e n l i k e t h e f o l l o wi n g .
Figure 16: Basic Settings Screen
D a t a - B a s i c S e t t i n g s S c r e e n
Operation
W i r e l e s s M o d e
S e l e c t t h e d e s i r e d o p t i o n :
• Disable - select this if for some reason you do not this AP to
transmit or receive at all.
• 802.11b and 802.11g - this is the default, and will allow
connections by both 802.11b and 802.1g wireless stations.
• 802.11b - if selected, only 802.11b connections are allowed.
802.11g wireless stations will only be able to connect if they
are fully backward-compatible with the 802.11b standard.
• 802.11g - only 802.11g connections are allowed. If you only
have 802.11g, selecting this option may provide a
performance improvement over using the default setting.
• Dynamic Super 802.11g (108Mbps) - This uses Packet
Bursting, FastFrame, Compression, and Channel Bonding
(using 2 channels) to increase throughput. Only clients
supporting the "Atheros Super G" mode can connect at
108Mbps, and they will only use this speed when necessary.
However, this option is backward-compatible with 802.11b
and (standard) 802.11g.
• Static Super 802.11g (108Mbps) - This uses Packet
Bursting, FastFrame, Compression, and Channel Bonding
(using 2 channels) to increase throughput.
Because "Channel Bonding" is always used, this
method is NOT compatible with 802.11b and (standard)
802.11g.
Only clients supporting the "Atheros Super G" mode can
connect at 108Mbps; they will always connect at this speed.
Page 27
P a g e 2 7 o f
9 3
Select this option only if all wireless stations support this
"Atheros Super G" mode.
A P M o d e
B o t h B r i d g e m o d e a n d A P m o d e c a n b e u s e d s i m u l t a n e o u s l y ,
u n l e s s A P m o d e i s " C l i e n t / R e p e a t e r " . S e l e c t t h e d e s i r e d A P m o d e :
• None (disable) - Disable AP mode. Use this if you want to
act a Bridge only.
• Access Point - operate as a normal Access Point
• Client/Repeater - act as a client or repeater for another
Access Point. If selected, you must provide the address
(MAC address) of the other AP in the Repeater AP MAC
Address field. In this mode, all traffic is sent to the specified
AP.
N o t e : I f u s i n g C l i e n t / R e p e a t e r m o d e , y o u c a n n o t u s e B r i d g e M o d e .
R e p e a t e r A P
M A C A d d r e s s
T h i s i s n o t r e q u i r e d u n l e s s t h e A P M o d e i s " C l i e n t / R e p e a t e r " . I n t h i s
m o d e , y o u m u s t p r o v i d e t h e M A C a d d r e s s o f t h e o t h e r A P i n t h i s
f i e l d . Y o u c a n e i t h e r e n t e r t h e M A C a d d r e s s d i r e c t l y , o r , i f t h e o t h e r
A P i s o n -l i n e a n d b r o a d c a s t i n g i t s S S I D , y o u c a n c l i c k t h e " S e l e c t
A P " b u t t o n a n d s e l e c t f r o m a l i s t o f a v a i l a b l e A P s .
B r o a d c a s t S S I D
I f D i s a b l e d , n o S S I D i s b r o a d c a s t .
I f e n a b l e d , y o u m u s t s e l e c t t h e s e c u r i t y p r o f i l e w h o s e S S I D i s t o b e
b r o a d c a s t . T h i s c a n b e d o n e t h e " S e c u r i t y P r o f i l e s " s c r e e n . T h e
S S I D w i l l t h e n b e b r o a d c a s t t o a l l W i r e l e s s S t a t i o n s . S t at i o n s w h i c h
h a v e n o S S I D ( o r a " n u l l " v a l u e ) c a n t h e n a d o p t t h e c o r r e c t S S I D f o r
c o n n e ct i o n s t o t h i s A c c e s s P o i n t .
B r i d g e M o d e
B o t h B r i d g e m o d e a n d A P m o d e c a n b e u s e d s i m u l t a n e o u s l y ,
u n l e s s A P m o d e i s " C l i e n t / R e p e a t e r " . S e l e c t t h e d e s i r e d B r i d g e
m o d e :
N o n e ( d i s a b l e ) - D i s a b l e B r i d g e m o d e . U s e t h i s i f y o u w a n t t o a c t a
A P o n l y .
P o i n t -t o -P o i n t B r i d g e ( P T P ) - B r i d g e t o a s i n g l e A P . Y o u m u s t
p r o v i d e t h e M A C a d d r e s s o f t h e o t h e r A P i n t h e P T P B r i d g e A P
M A C A d d r e s s f i e l d .
P o i n t -t o -M u l t i -P o i n t B r i d g e ( P T M P ) - S e l e c t t h i s o n l y i f t h i s A P i s
t h e " M a s t e r " f o r a g r o u p o f B r i d g e -m o d e A P s . T h e o t h e r B r i d g e m o d e A P s m u s t b e s e t t o P o i n t -t o -P o i n t B r i d g e m o d e , u s i n g t h i s
A P ' s M A C a d d r e s s . T h e y t h e n s e n d a l l t r a ff i c t o t h i s " M a s t e r " .
I f r e q u i r e d , y o u c a n s p e c i f y t h e M A C a d d r e s s e s o f t h e A P s w h i c h
a r e a l l o w e d t o c o n n e c t t o t h i s A P i n P T M P m o d e . T o s p e c i f y t h e
all o w e d A P s :
4 5 . E n a b l e t h e c h e c k b o x " I n P T M P m o d e , o n l y a l l o w s p e c i f i e d
A P s " .
C l i c k t h e b u t t o n " S e t P T M P A P s " .
O n t h e r e s u l t i n g s u b -s c r e e n , e n t e r t h e M A C a dd r e s s e s o f t h e
a l l o w e d A P s .
P T P B r i d g e A P
M A C A d d r e s s
T h i s i s n o t r e q u i r e d u n l e s s t h e B r i d g e M o d e i s " P o i n t -t o -P o i n t B r i d g e
( P T P ) " . I n t h i s c a s e , y o u m u s t e n t e r t h e M A C a d d r e s s o f t h e o t h e r
A P i n t h i s f i e l d .
I n P T M P m o d e ,
o n l y a l l o w
s p e c if i e d A P s
T h i s i s o n l y f u n c t i o n a l i f u s i n g P o i n t -t o -M u l t i -P o i n t B r i d g e ( P T M P )
m o d e . I f e n a b l e d , y o u c a n s p e c i f y t h e M A C a d d r e s s e s o f t h e A P s
w h i c h a r e a l l o w e d t o c o n n e c t t o t h i s A P . T o s p e c i f y t h e a l l o w e d A P s :
4 6 . E n a b l e t h i s c h e c k b o x
C l i c k t h e b u t t o n " S e t P T M P A P s " .
O n t h e r e s u l t i n g s u b -s c r e e n , e n t e r t h e M A C a d d r e s s e s o f t h e
a l l o w e d A P s .
S e t P T M P A P s
U s e t h i s t o o p e n a s u b -w i n d o w w h e r e y o u c a n s p e c i f y t h e M A C
add r e s s e s o f t h e A P s w h i c h a r e a l l o w e d t o c o n n e c t t o t h i s A P . T h i s
i s o n l y f u n c t i o n a l i f u s i n g P o i n t -t o -M u l t i -P o i n t B r i d g e ( P T M P ) m o d e
a n d y o u h a v e e n a b l e d t h e c h e c k b o x " I n P T M P m o d e , o n l y a l l o w
s p e c i f i e d A P s " .
Page 28
P a g e 2 8 o f
9 3
Parameters
C h a n n e l N o
• If "Automatic" is selected, the Access Point will select the
best available Channel.
• If you experience interference (shown by lost connections
and/or slow data transfers) you may need to experiment with
manually setting different channels to see which is the best.
C u r r e n t
C h a nn e l N o .
T h i s d i s p l a y s t h e c u r r e n t c h a n n e l u s e d b y t h e A c c e s s P o i n t .
Page 29
P a g e 2 9 o f
9 3
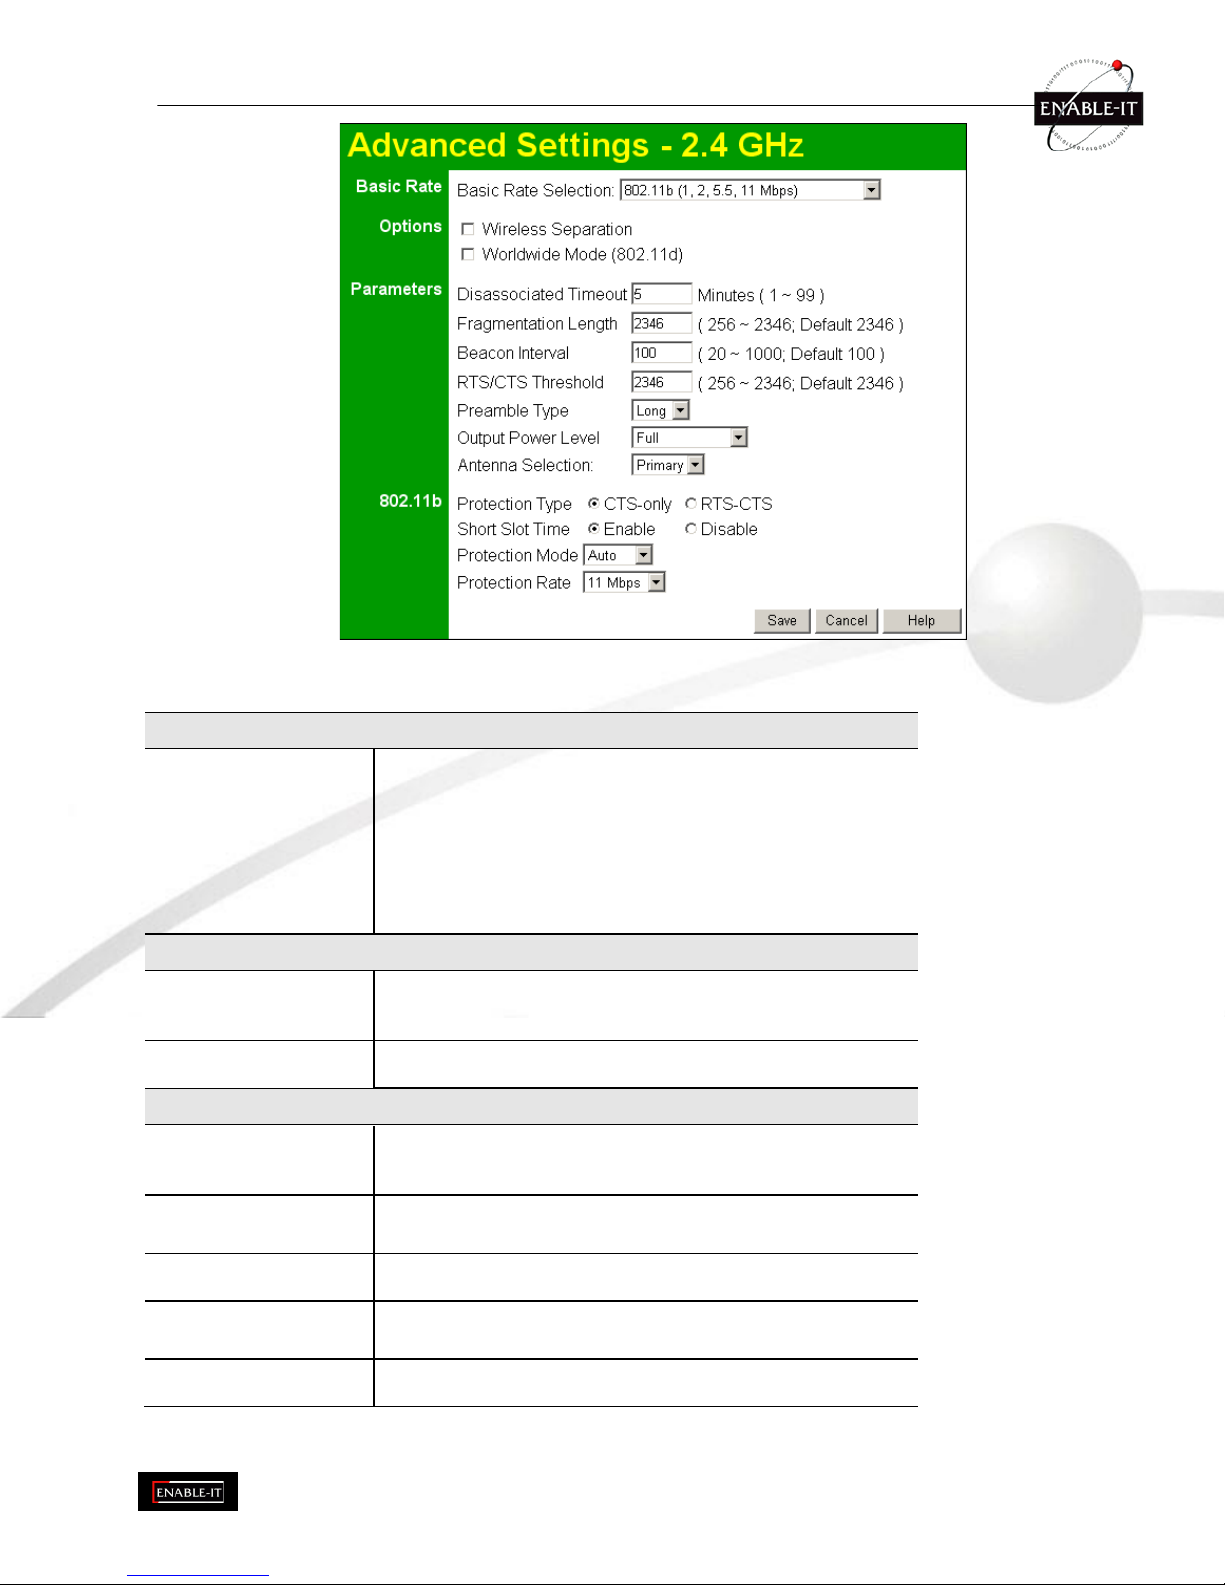
A d v a n c e d S e t t i n g s
C l i c k i n g t h e A d v a n c e d l i n k o n t h e m e n u w i l l r e s u l t i n a s c r e e n l i k e t h e f o l l o w i n g .
Figure 17: Advanced Settings
D a t a - A d v a n c e d S e t t i n g s S c r e e n
Basic Rate
B a s i c R a t e
T h e B a s i c R a t e i s u s e d f o r b r o a d c a s t i n g . I t d o e s n o t
d e t e r m i n e t h e d a t a t r a n s m i s s i o n r a t e , w h i c h i s d e t e r m i n e d b y
t h e " M o d e " s e t t i n g o n t h e B a s i c s c r e e n .
S e l e c t t h e d e s i r e d o p t i o n .
D o N O T s e l e c t t h e " 8 0 2 . 1 1 g " o r " O D F M " o p t i o n s u n l e s s A L L
o f y o u r w i r e l e s s c l i e n t s s u p p o r t t h i s . 8 0 2 . 1 1 b c l i e n t s w i l l n o t b e
a b l e t o c o n n e c t t o t h e A c c e s s P o i n t i f e i t h e r o f t h e s e m o d e s i s
s e l e c t e d .
Options
W i r e l e s s S e p a r a t i o n
I f e n a b l e d , t h e n e a c h W i r e l e s s s t a t i o n u s i n g t h e A c c e s s P o i n t
i s i n v i s i b l e t o o t h e r W i r e l e s s s t a t i o n s . I n m o s t b u s in e s s
s i t u a t i o n s , t h i s s e t t i n g s h o u l d b e D i s a b l e d .
W o r l d w i d e M o d e
( 8 0 2 . 1 1 d )
E n a b l e t h i s s e t t i n g i f y o u w i s h t o u s e t h i s m o d e , a n d y o u r
W i r el e s s s t a t i o n s s u p p o r t t h i s m o d e .
Parameters
D i s a s s o c i a t e d
T i m eo u t
T h i s d e t e r m i n e s h o w q u i c k l y a W i r e l e s s S t a t i o n w i l l b e
c o n s i de r e d " D i s a s s o c i a t e d " w i t h t h i s A P , w h e n n o t r a f f i c i s
r e c e i v e d . E n t e r t h e d e s i r e d t i m e p e r i o d .
F r a g m e n t a t i o
n
E n t e r t h e p r e f e r r e d s e t t i n g b e t w e e n 2 5 6 a n d 2 3 4 6 . N o rm a l l y ,
t h i s c a n b e l e f t a t t h e d e f a u l t v a l u e .
B e a c o n I n t e r v a l
E n t e r t h e p r e f e r r e d s e t t i n g b e t w e e n 2 0 a n d 1 0 0 0 . N o rm a l l y ,
t h i s c a n b e l e f t a t t h e d e f a u l t v a l u e .
R T S / C T S
T h r e s h o l d
E n t e r t h e p r e f e r r e d s e t t i n g b e t w e e n 2 5 6 a n d 2 3 4 6 . N o rm a l l y ,
t h i s c a n b e l e f t a t t h e d e f a u l t v a l u e .
P r e a m b l e T y p e
S e l e c t t h e d e s i r e d o p t i o n . T h e d e f a u l t i s " L o n g " . T h e " S h o r t "
s e t t i n g t a k e s l e s s t i m e w h e n u s e d i n a g o o d e n v ir o n m e n t .
Page 30
P a g e 3 0 o f
9 3
O u t p u t P o w e r L e v e l
S e l e c t t h e d e s i r e d p o w e r o u t p u t . H i g h e r l e v e l s w i l l g i v e a
g r e a t e r r a n g e , b u t a r e a l s o m o r e l i k e l y t o c a u s e i n t e r f e re n c e
w i t h o t h e r d e v i c e s .
A n t e n n a S e l e c t i o n
I f y o u r A c c e s s P o i n t h a s o n l y 1 a n t e n n a , t h e r e i s o n l y 1 o p t i o n
a v a i l a b l e . I f y o u r A c c e s s P o i n t h a s 2 a n t e n n a e , s e l e c t t h e
o p t i o n w h i c h g i v e s t h e b e s t r e s u l t s i n y o u r l o c a t i o n .
802.11b
P r o t e c t i o n
T y p e
S e l e c t t h e d e s i r e d o p t i o n . T h e d e f a u l t i s C T S -o n l y .
S h o r t S l o t T i m e
E n a b l e o r d i s a b l e t h i s s e t t i n g a s r e q u i r e d .
P r o t e c t i o n
M o d e
T h e P r o t e c t i o n s y s t e m i s i n t e n d e d t o p r e v e n t o l d e r 8 0 2 . 1 1 b
d e v i c e s f r o m i n t e r f e r i n g w i t h 8 0 2 . 1 1 g t r a n s m i ss i o n s . ( O l d e r
8 0 2 . 1 1 b d e v i c e s m a y n o t b e a b l e t o d e t e c t t h a t a 8 0 2 . 1 1 g
t r a n sm i s s i o n i s i n p r o g r e s s . ) N o r m a l l y , t h i s s h o u l d b e l e f t a t
" A u t o " .
P r o t e c t i o n R a t e
S e l e c t t h e d e s i r e d o p t i o n . T h e d e f a u l t i s 1 1 M b p s .
Page 31
P a g e 3 1 o f
9 3
C h a p t e r 4
P C a n d S e r v e r C o n f i g u r at i o n
This Chapter details the PC Configuration required for each PC on the local LAN.
O v e r v i e w
A l l W i r e l e s s S t a t i o n s n e e d t o h a v e s e t t i n g s w h i c h m a t c h t h e W i r e l e s s A c c e s s P o i n t . T h e s e s e t t i n g s d e p e n d o n t h e m o d e
i n w h i c h t h e A c c e s s P o i n t i s b e i n g u s e d .
• If using WEP or WPA-PSK, it is only necessary to ensure that each Wireless station's settings match those of
the Wireless Access Point, as described below.
• For WPA-802.1x and 802.1x modes, configuration is much more complex. The Radius Server must be
configured correctly, and setup of each Wireless station is also more complex.
U s i n g W E P
F o r e a c h o f t h e f o l l o w i n g i t e m s , e a c h W i r e l e s s S t a t i o n m u s t h a v e t h e s a m e s e t t i n g s a s t h e W i r e l e s s A c c e s s P o i n t .
M o d e
O n e a c h P C , t h e m o d e m u s t b e s e t t o I n f r a s t r u ct u r e .
S S I D ( E S S I D )
T h i s m u s t m a t c h t h e v a l u e u s e d o n t h e W i r e l e s s A c c e s s P o i n t .
T h e d e f a u l t v a l u e i s w i r e l e s s
N o t e ! T h e S S I D i s c a s e s e n s i t i v e .
W i r e l e s s
S e c u r i t y
• Each Wireless station must be set to use WEP data
encryption.
• The Key size (64 bit, 128 bit, 152 bit) must be set to match the
Access Point.
• The keys values on the PC must match the key values on the
Access Point.
N o t e :
O n s o m e s y s t e m s , t h e k e y s i z e s m a y b e s h o w n a s 4 0 b i t , 1 0 4 b i t , a n d
1 2 8 b i t i n s t e a d o f 6 4 b i t , 1 2 8 b i t a n d 1 5 2 b i t . T h i s d i f f e r e n c e a r i s e s
bec a u s e t h e k e y i n p u t b y t h e u s e r i s 2 4 b i t s l e s s t h a n t h e k e y s i z e
u s e d f o r e n c r y pt i o n .
Page 32
P a g e 3 2 o f
9 3
U s i n g W P A -8 0 2 . 1 x
T h i s i s t h e m o s t s e c u r e a n d m o s t c o m p l e x s y s t e m .
8 0 2 . 1 x m o d e p r o v i d e s g r e a t e r s e c u r i t y a n d c e n t r a l i z e d m a n a g e m e n t , b u t i t i s m o r e c o m p l e x t o c o n f i g u r e .
Wireless Station Configuration
F o r e a c h o f t h e f o l l o w i n g i t e m s , e a c h W i r e l e s s S t a t i o n m u s t h a v e t h e s a m e s e t t i n g s a s t h e W i r e l e s s A c c e s s P o i n t .
M o d e
O n e a c h P C , t h e m o d e m u s t b e s e t t o I n f r a s t r u ct u r e .
S S I D ( E S S I D )
T h i s m u s t m a t c h t h e v a l u e u s e d o n t h e W i r e l e s s A c c e s s P o i n t .
T h e d e f a u l t v a l u e i s wir e l e s s
N o t e ! T h e S S I D i s c a s e s e n s i t i v e .
8 0 2 . 1 x
A u t h e nt i c at i o n
E a c h c l i e n t m u s t o b t a i n a C e r t i f i c a t e w h i c h i s u s e d f o r a u t h e n t i c at i o n
f o r t h e R a d i u s S e r v e r .
8 0 2 . 1 x
E n c r y p t i o n
T y p i c a l l y , E A P -T L S i s u s e d . T h i s i s a d y n a m i c k e y s y s t e m , s o k e y s d o
N O T h a v e t o b e e n t e r e d o n e a c h W i r e l e s s s t a t i o n .
H o w e v e r , y o u c a n a l s o u s e a s t a t i c W E P k e y ( E A P -M D 5 ) ; t h e
W i r e l e s s A c c e s s P o i n t s u p p o r t s b o t h m e t h o d s s i m u l t a n e o u s l y .
Radius Server Configuration
I f u s i n g W P A -8 0 2 . 1 x m o d e , t h e R a d i u s S e r v e r o n y o u r n e t w o r k m u s t b e c o n f i g u r e d a s f o l l o w :
• It must provide and accept Certificates for user authentication.
• There must be a Client Login for the Wireless Access Point itself.
• The Wireless Access Point will use its Default Name as its Client Login name. (However, your Radius
server may ignore this and use the IP address instead.)
• The Shared Key, set on the Security Screen of the Access Point, must match the Shared Secret value on
the Radius Server.
• Encryption settings must be correct.
Page 33
P a g e 3 3 o f
9 3
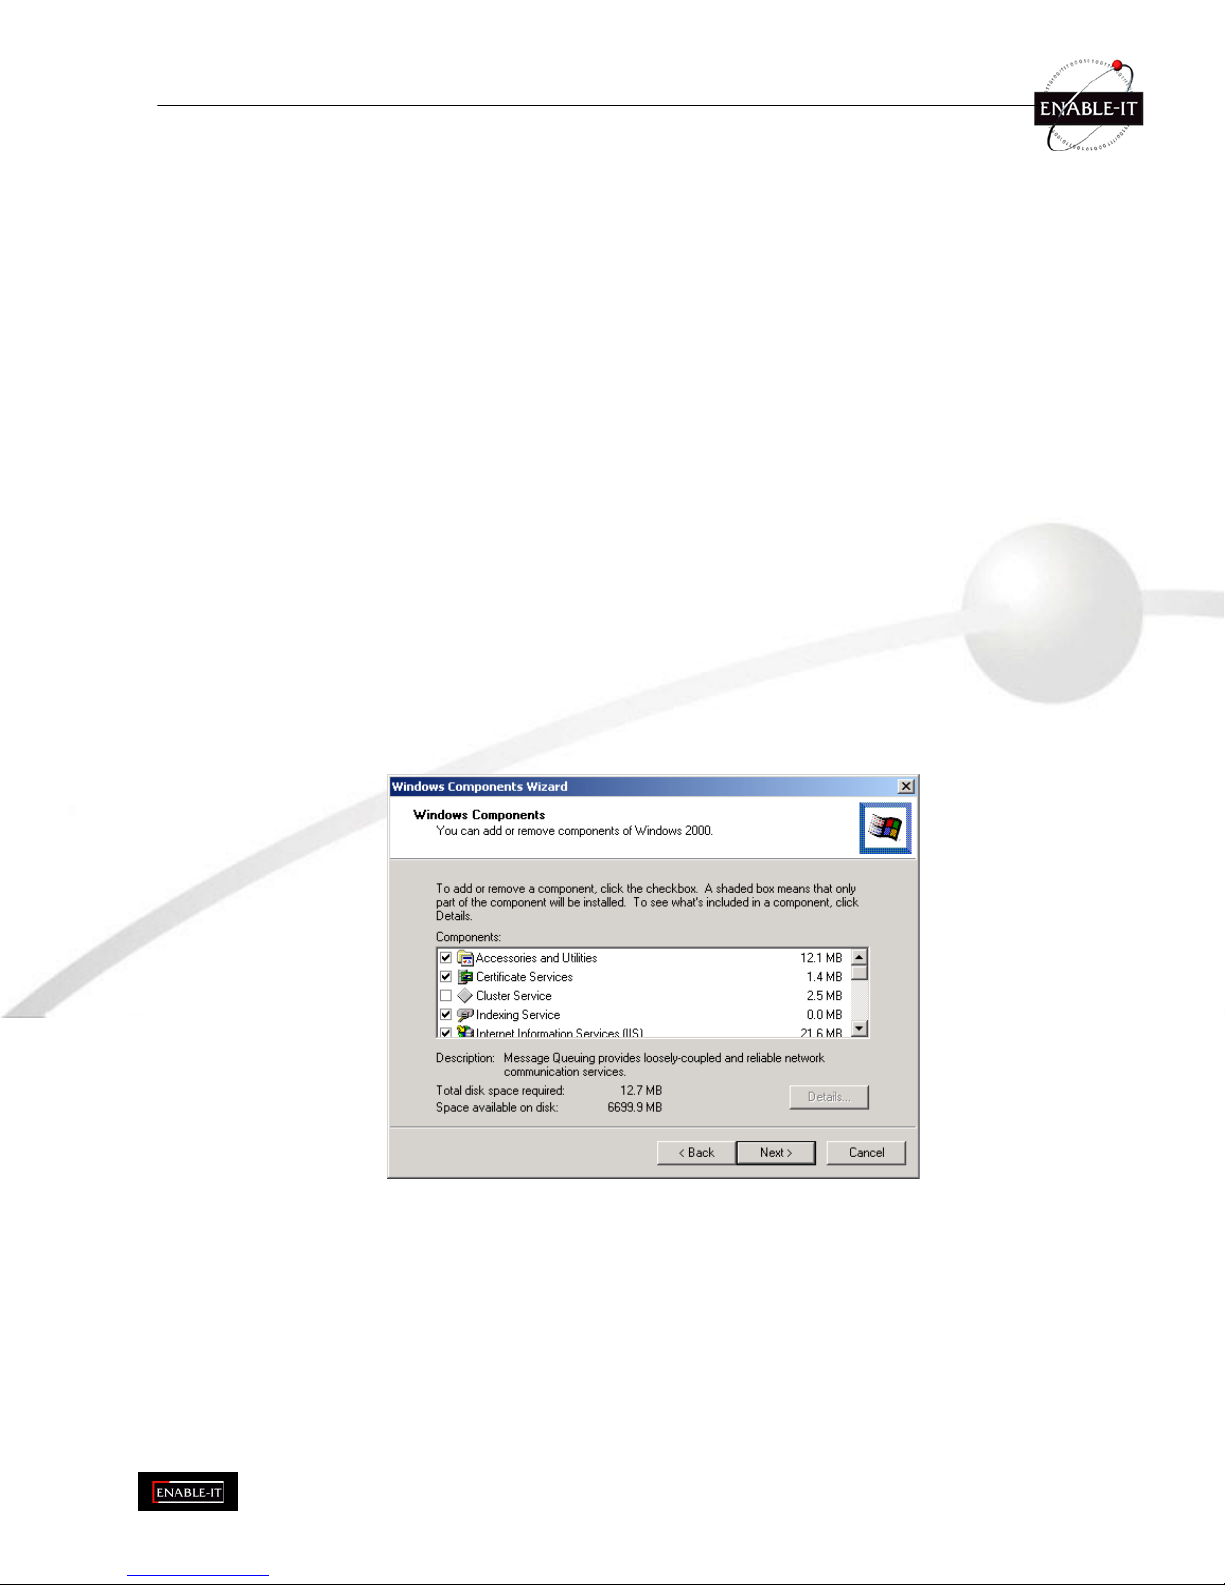
8 0 2 . 1 x S e r v e r S e t u p ( W i n d o w s 2 0 0 0 S e r v e r )
T h i s s e c t i o n d e s c r i b e s u s i n g M i c r o s o f t I n t e r n e t A u t h e n t i c a t i o n S e r v e r a s t h e R a d i u s S e r v e r , s i n c e i t i s t h e m o s t c o m m o n
R a d i u s S e r v e r a v a i l a b l e t h a t s u p p o r t s t h e E A P -T L S a u t h e n t i c a t i o n m e t h o d .
T h e f o l l o w i n g s e r v i c e s o n t h e W i n d o w s 2 0 0 0 D o m a i n C o n t r o l l e r ( P D C ) a r e a l s o r eq u i r e d :
• dhcpd
• dns
• rras
• webserver (IIS)
• Radius Server (Internet Authentication Service)
• Certificate Authority
W i n d o w s 2 0 0 0 D o m a i n C o n t r o l l e r S e t u p
47. Run dcpromo.exe from the command prompt.
48. Follow all of the default prompts, ensure that DNS is installed and enabled during installation.
S e r v i c e s I n s t a l l a t i o n
49. Select the Control Panel - Add/Remove Programs.
50. Click Add/Remove Windows Components from the left side.
51. Ensure that the following components are activated (selected):
• Certificate Services. After enabling this, you will see a warning that the computer cannot be renamed and
joined after installing certificate services. Select Yes to select certificate services and continue
• World Wide Web Server. Select World Wide Web Server on the Internet Information Services (IIS)
component.
• From the Networking Services category, select Dynamic Host Configuration Protocol (DHCP), and
Internet Authentication Service (DNS should already be selected and installed).
Figure 18: Components Screen
52. Click Next.
53. Select the Enterprise root CA, and click Next.
Page 34
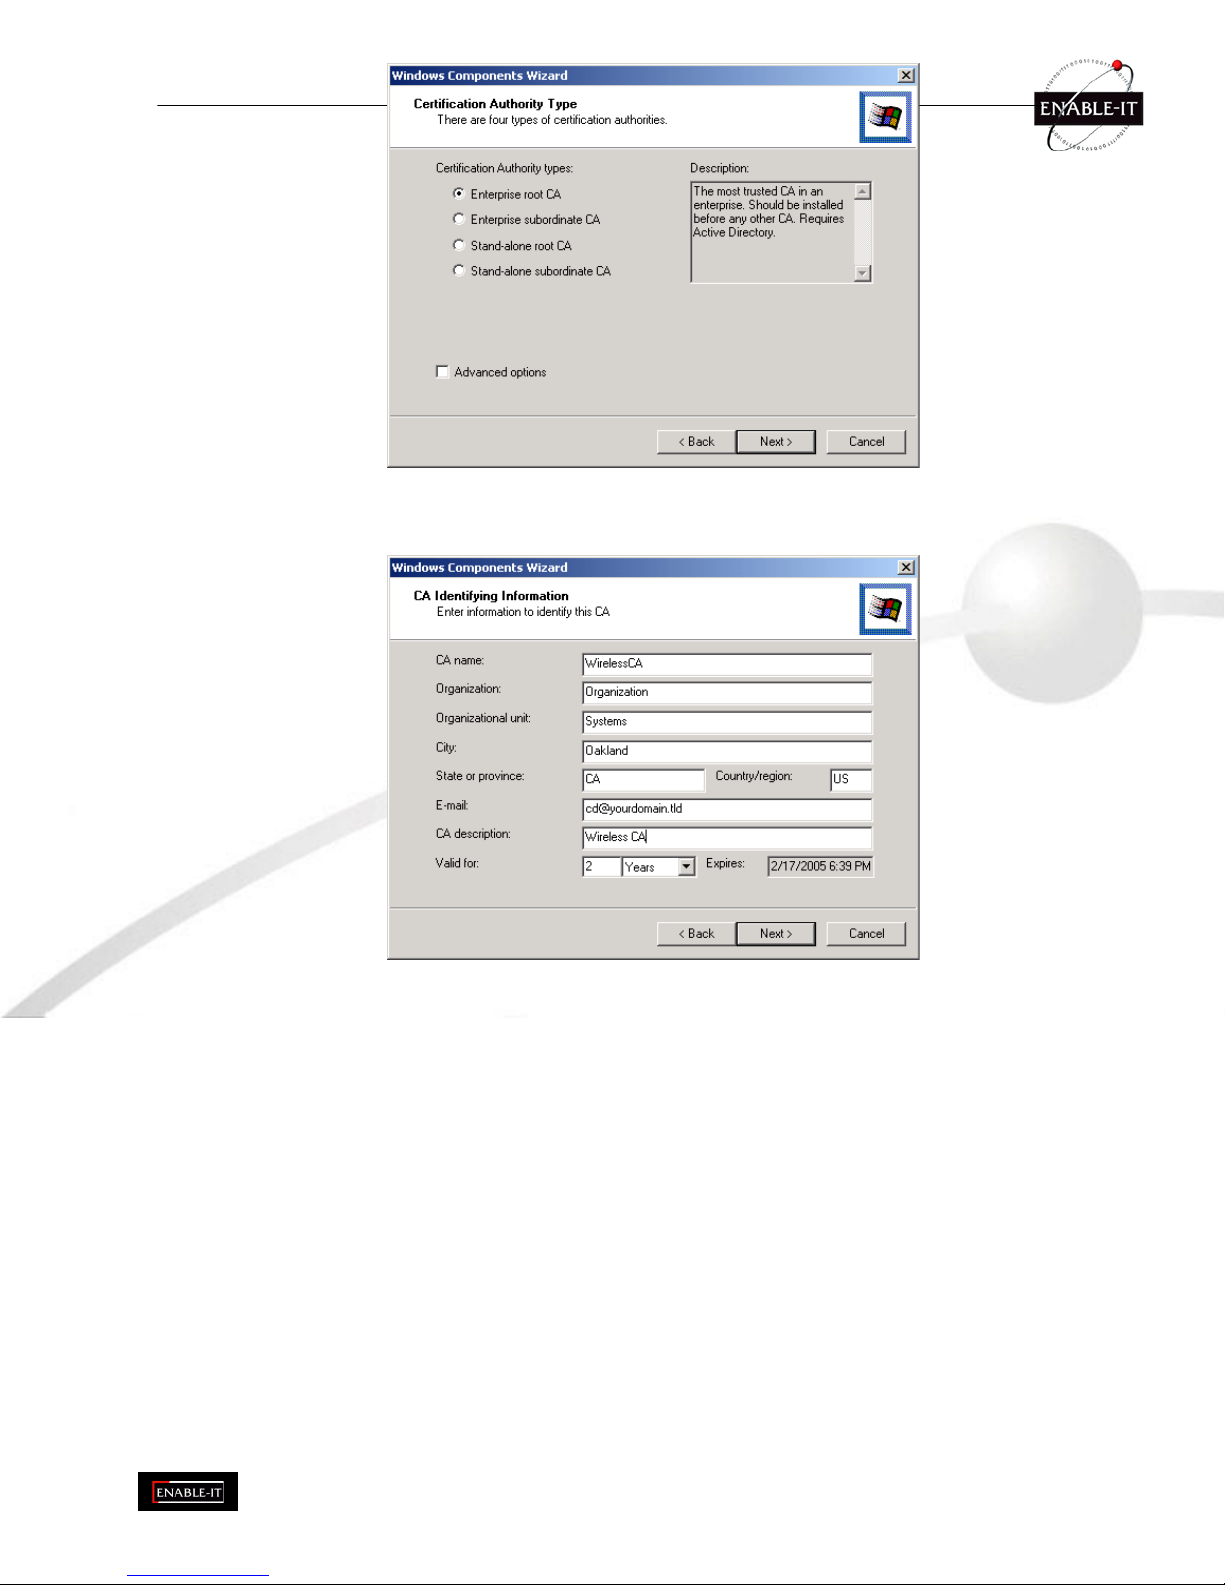
P a g e 3 4 o f
9 3
Figure 19: Certification Screen
54. Enter the information for the Certificate Authority, and click Next.
Figure 20: CA Screen
55. Click Next if you don't want to change the CA's configuration data.
56. Installation will warn you that Internet Information Services are running, and must be stopped before
continuing. Click Ok, then Finish.
D H C P s e r v e r c o n f i g u r a t i o n
57. Click on the Start - Programs - Administrative Tools - DHCP
58. Right-click on the server entry as shown, and select New Scope.
Page 35
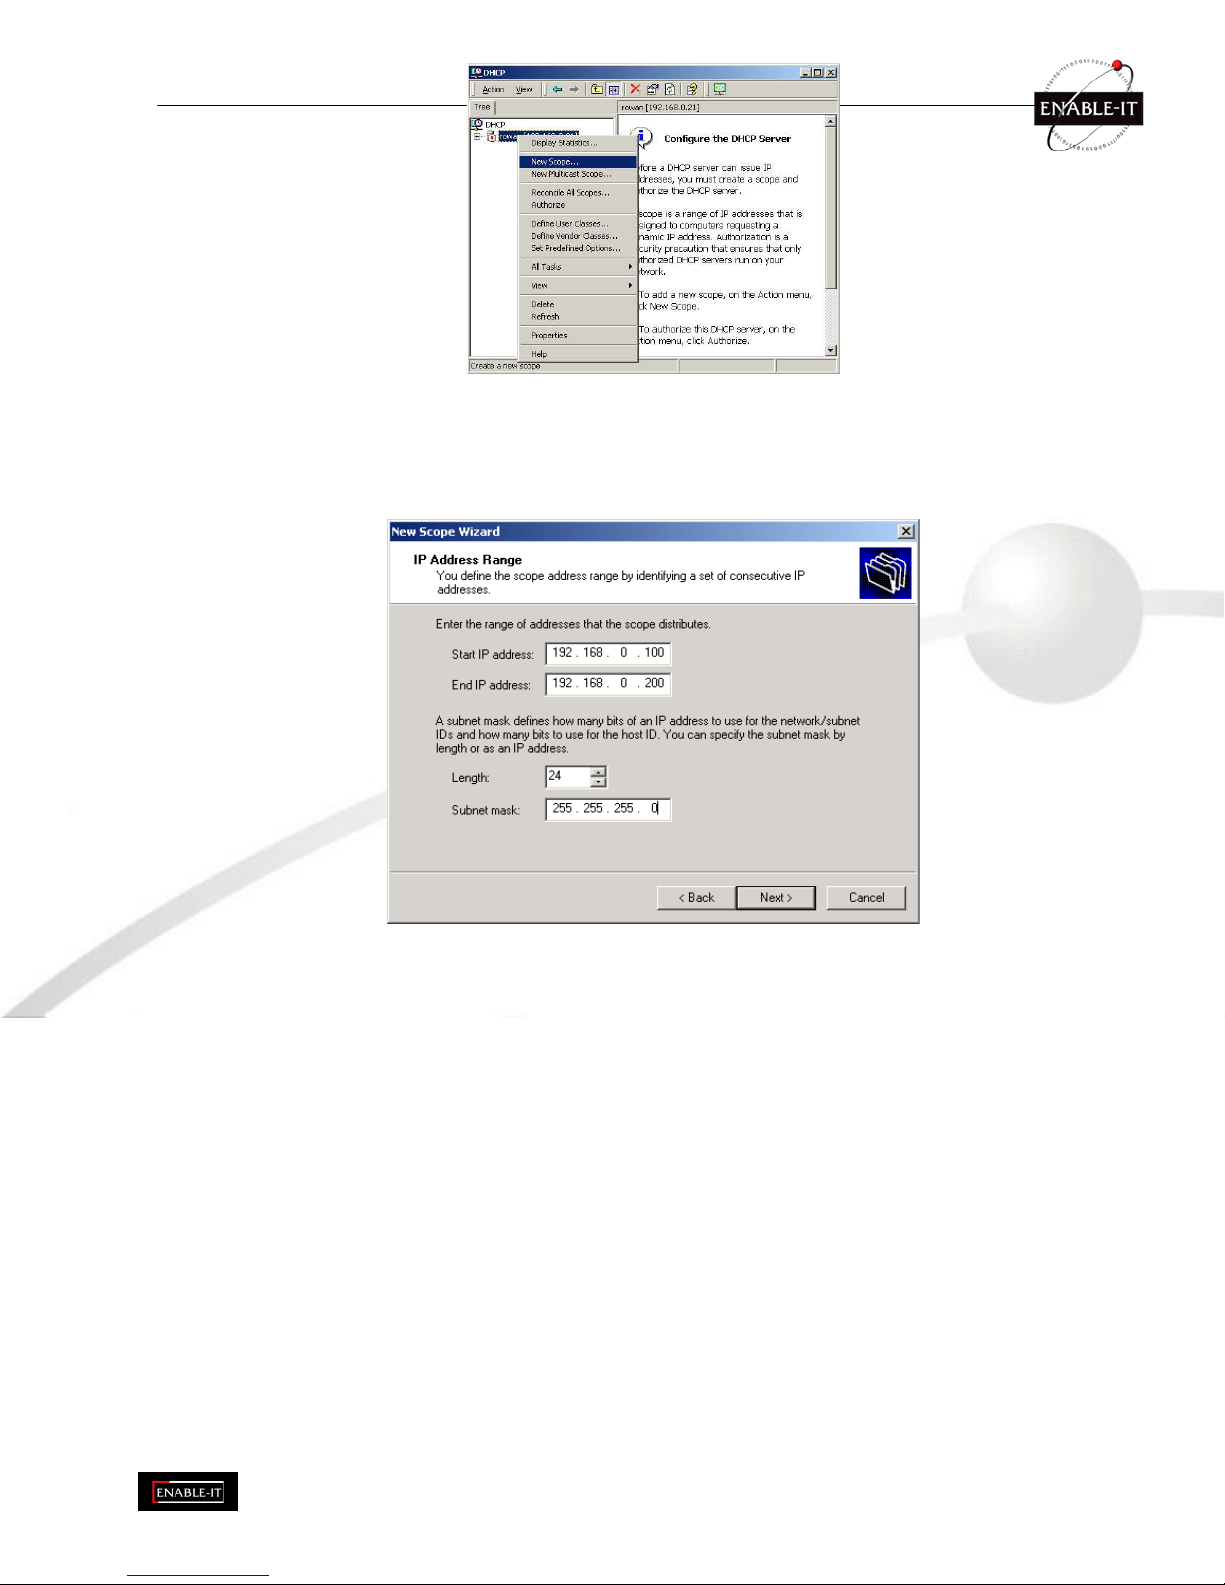
P a g e 3 5 o f
9 3
Figure 21: DHCP Screen
59. Click Next when the New Scope Wizard Begins.
60. Enter the name and description for the scope, click Next.
61. Define the IP address range. Change the subnet mask if necessary. Click Next.
Figure 22:IP Address Screen
62. Add exclusions in the address fields if required. If no exclusions are required, leave it blank. Click Next.
63. Change the Lease Duration time if preferred. Click Next.
64. Select Yes, I want to configure these options now, and click Next.
65. Enter the router address for the current subnet. The router address may be left blank if there is no router.
Click Next.
66. For the Parent domain, enter the domain you specified for the domain controller setup, and enter the server's
address for the IP address. Click Next.
Page 36
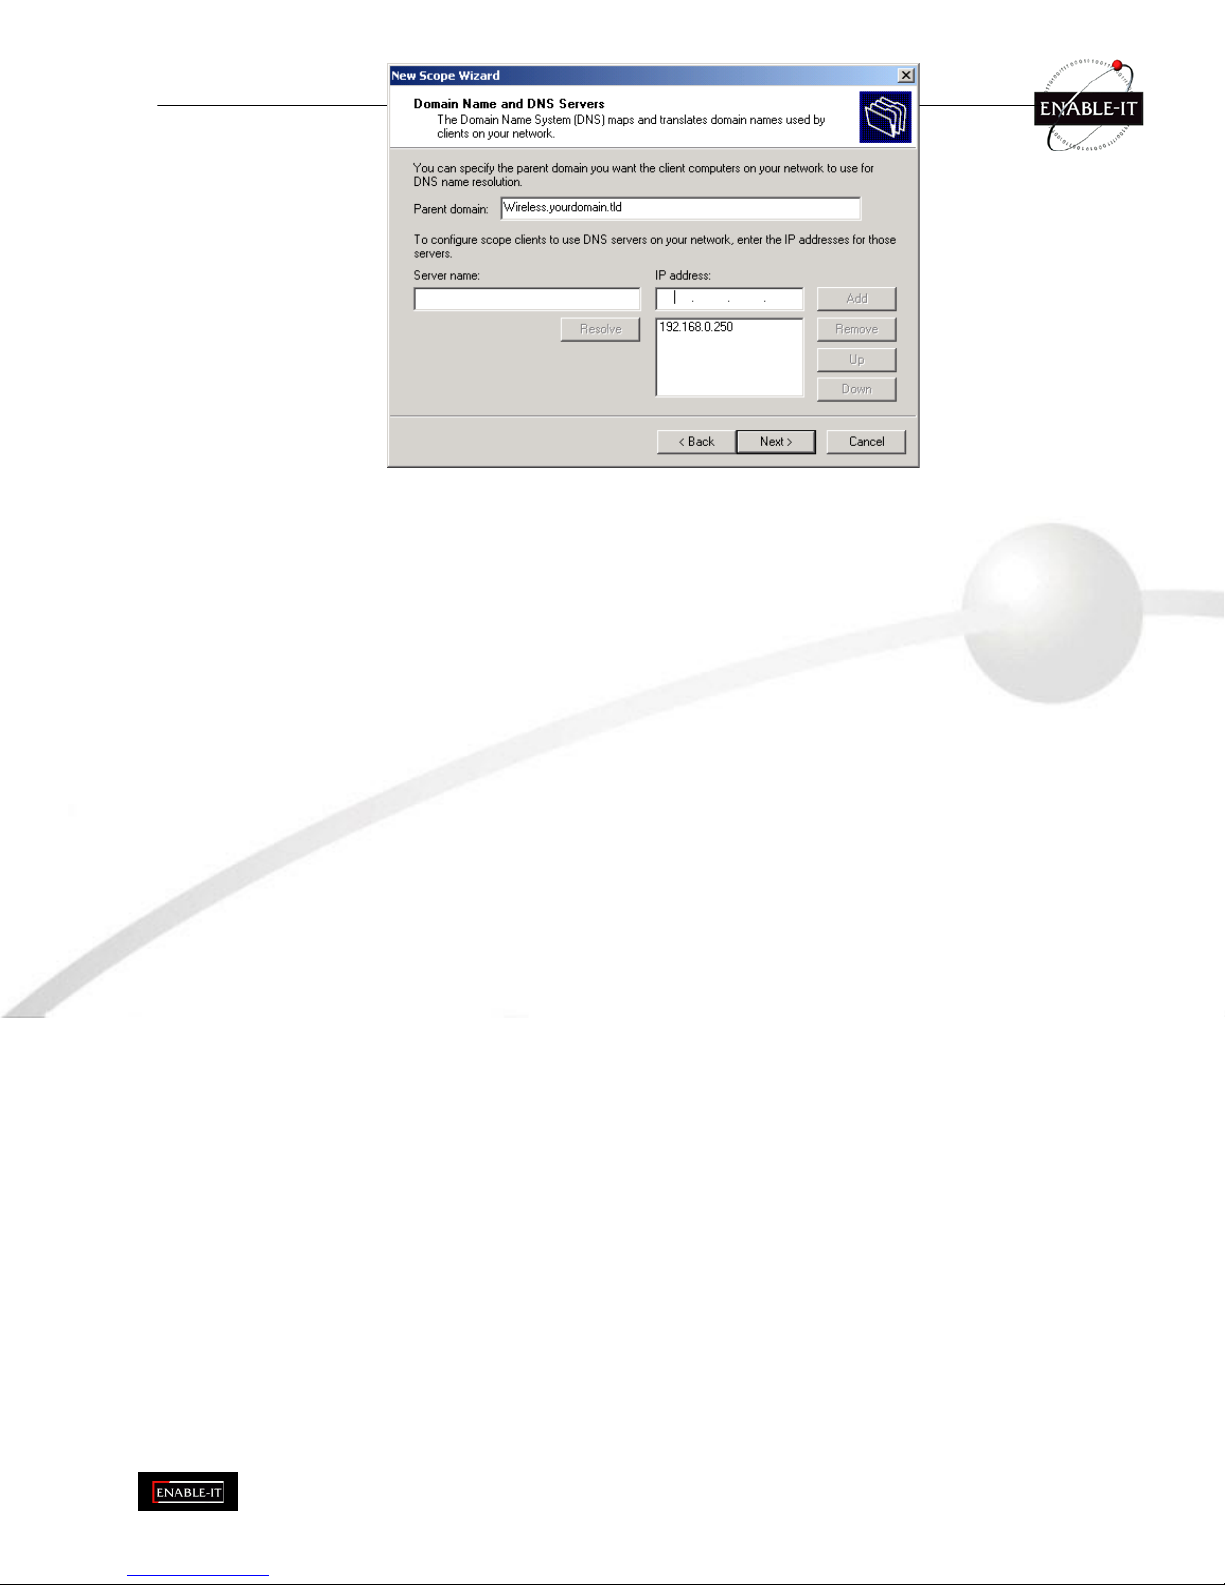
P a g e 3 6 o f
9 3
Figure 23: DNS Screen
67. If you don't want a WINS server, just click Next.
68. Select Yes, I want to activate this scope now. Click Next, then Finish.
69. Right-click on the server, and select Authorize. It may take a few minutes to complete.
Page 37
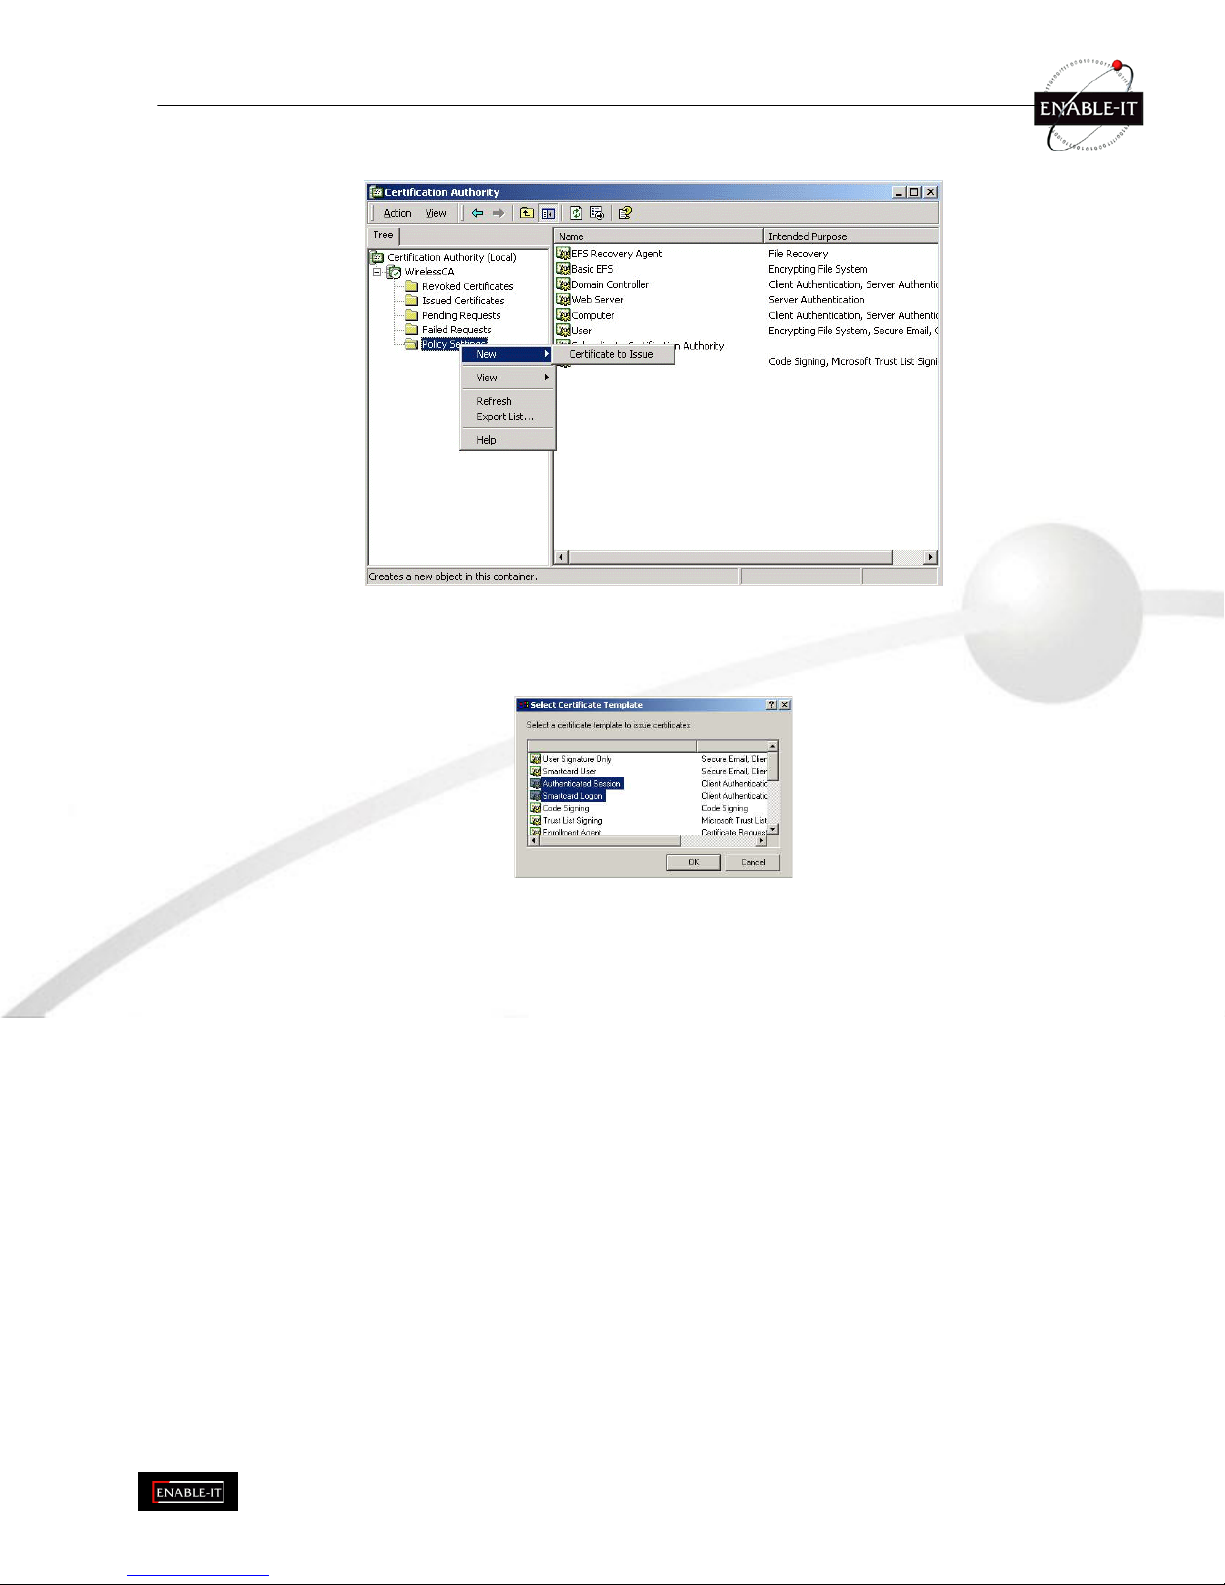
P a g e 3 7 o f
9 3
C e r t i f i c a t e A u t h o r i t y S e t u p
70. Select Start - Programs - Administrative Tools - Certification Authority.
71. Right-click Policy Settings, and select New - Certificate to Issue.
Figure 24: Certificate Authority Screen
72. Select Authenticated Session and Smartcard Logon (select more than one by holding down the Ctrl key).
Click OK.
Figure 25: Template Screen
73. Select Start - Programs - Administrative Tools - Active Directory Users and Computers.
74. Right-click on your active directory domain, and select Properties.
Page 38
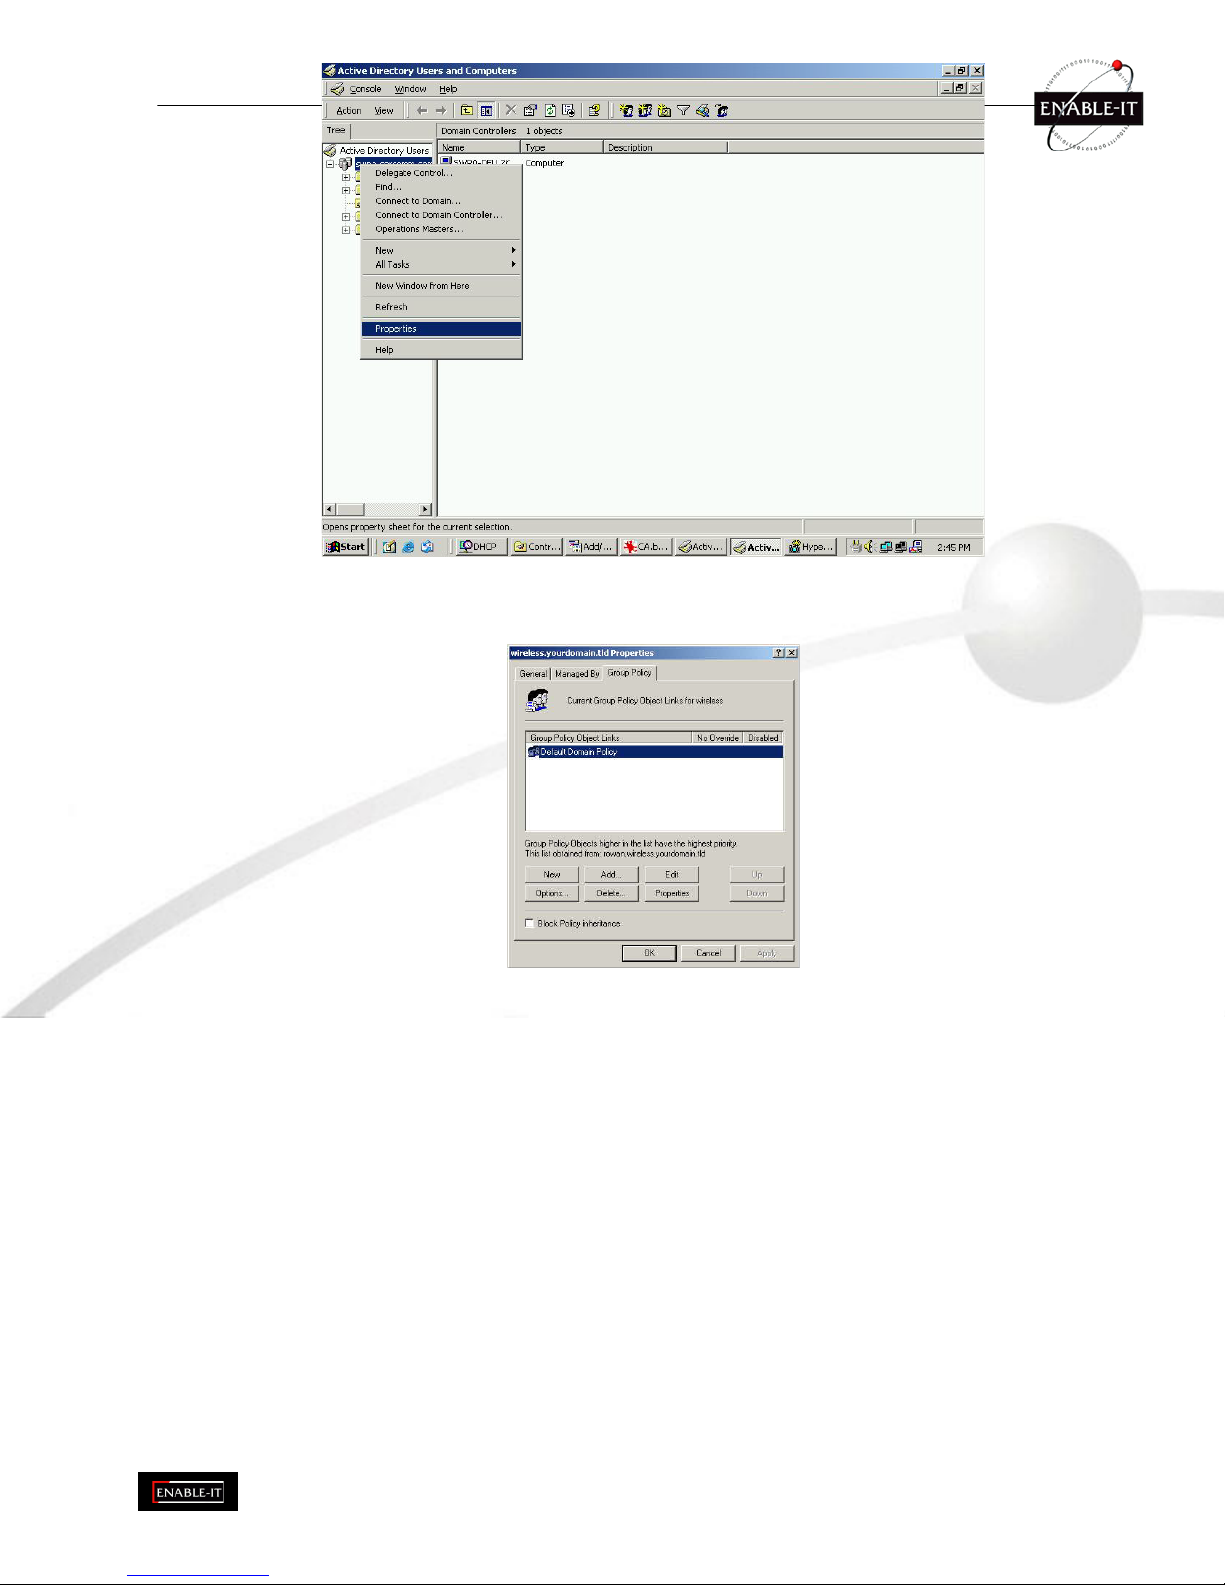
P a g e 3 8 o f
9 3
Figure 26: Active Directory Screen
75. Select the Group Policy tab, choose Default Domain Policy then click Edit.
Figure 27: Group Policy Tab
76. Select Computer Configuration - Windows Settings - Security Settings - Public Key Policies, right-click
Automatic Certificate Request Settings - New - Automatic Certificate Request.
Page 39
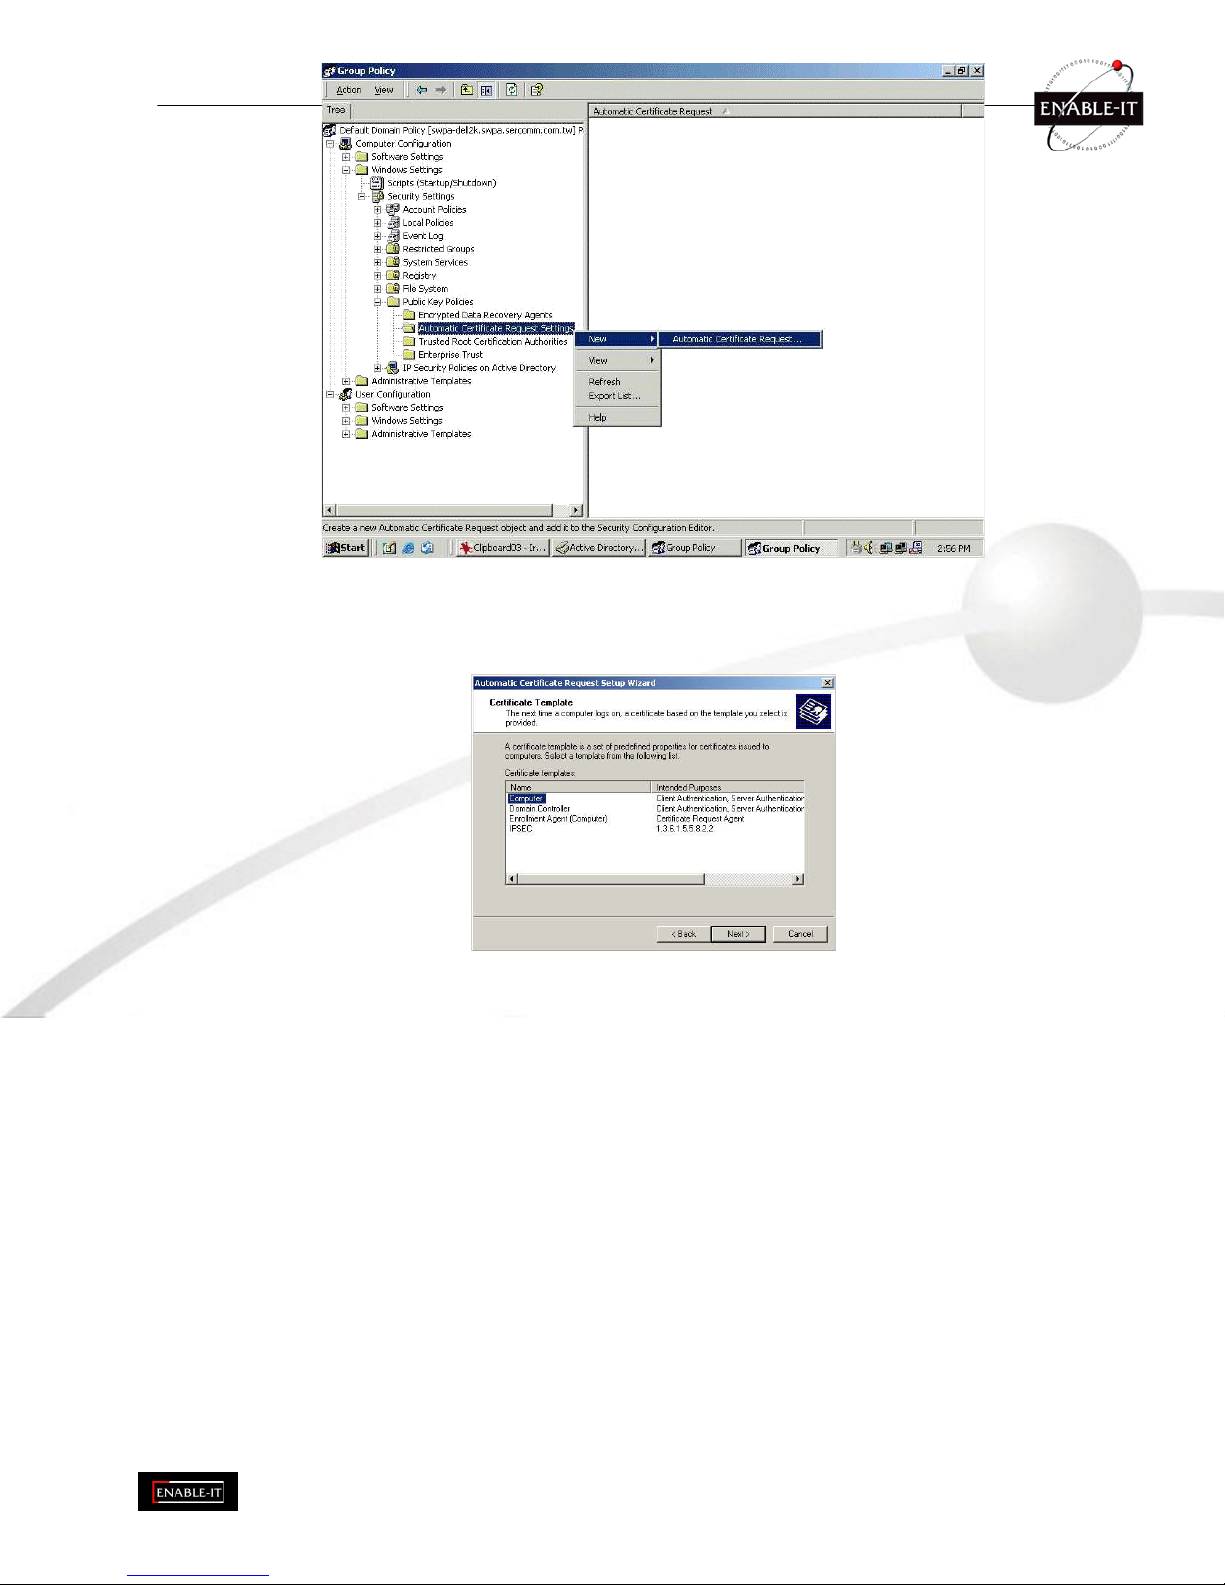
P a g e 3 9 o f
9 3
Figure 28: Group Policy Screen
77. When the Certificate Request Wizard appears, click Next.
78. Select Computer, then click Next.
Figure 29: Certificate Template Screen
79. Ensure that your certificate authority is checked, then click Next.
80. Review the policy change information and click Finish.
81. Click Start - Run, type cmd and press enter.
Enter secedit /refreshpolicy machine_policy
This command may take a few minutes to take effect.
Page 40
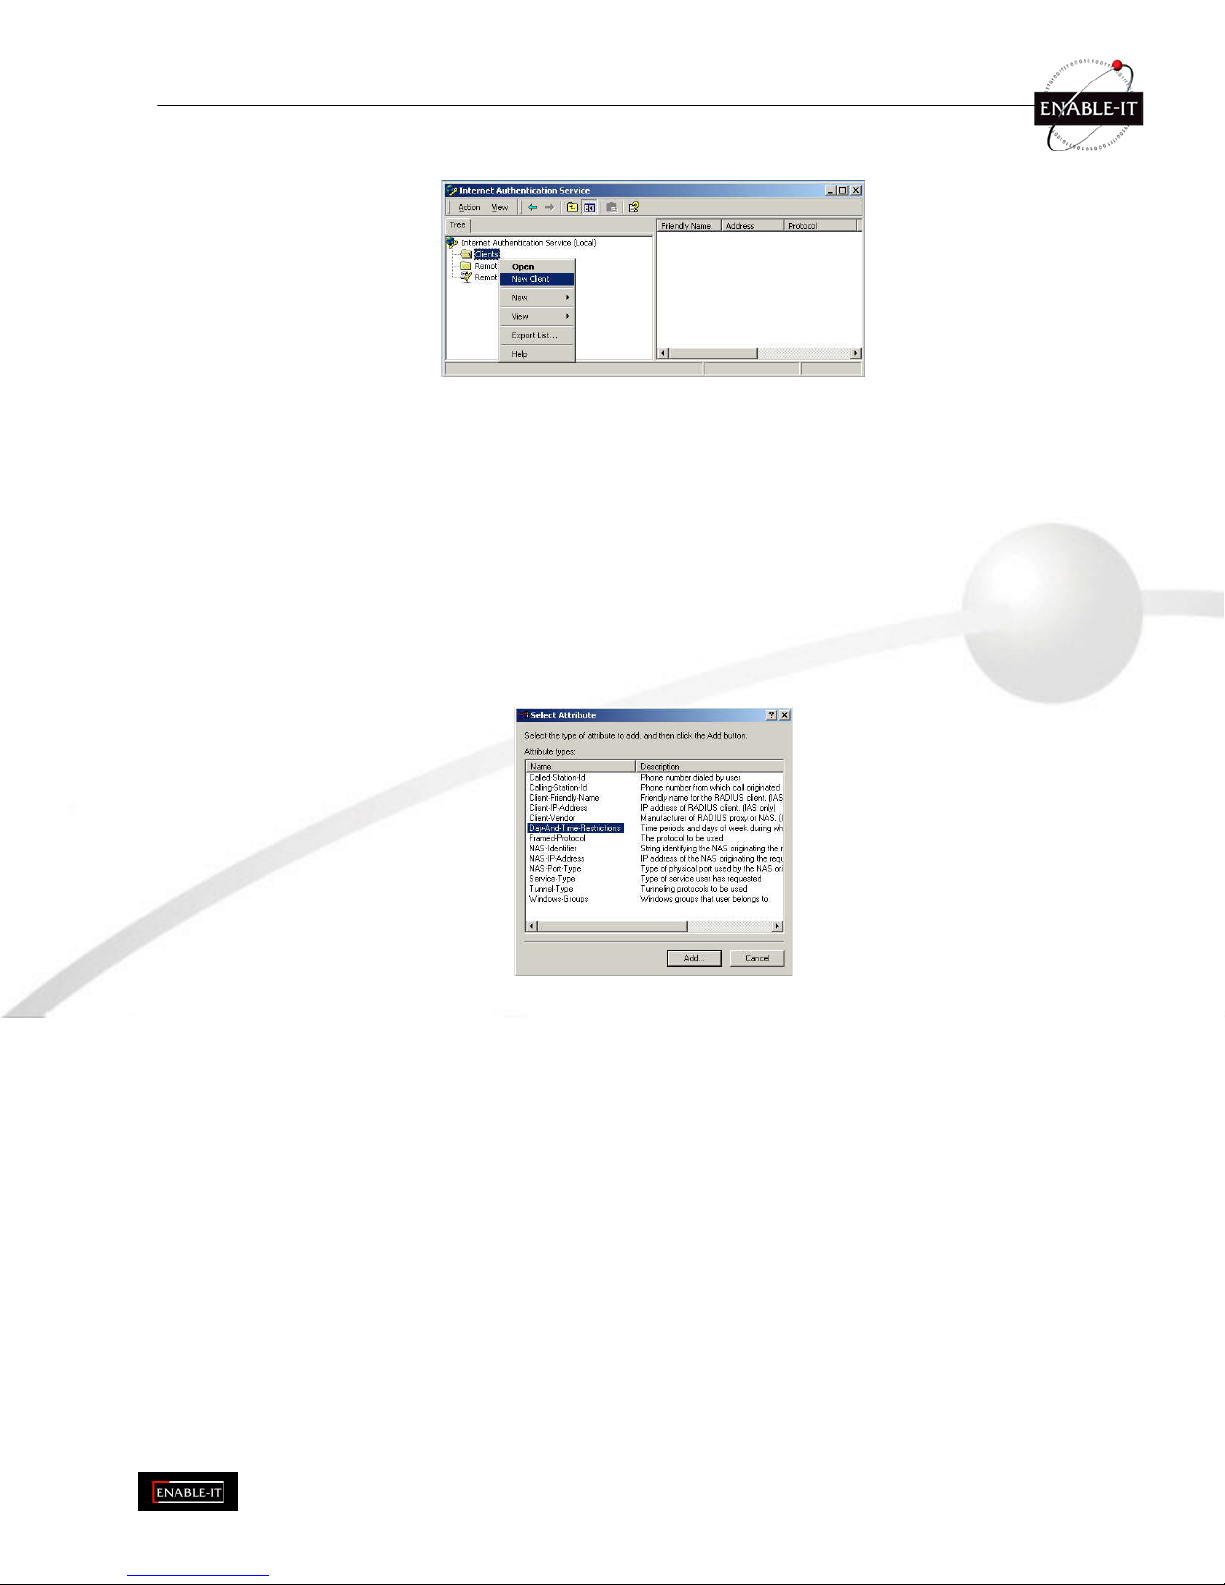
P a g e 4 0 o f
9 3
I n t e r n e t A u t h e n t i c a t i o n S e r v i c e ( R a d i u s ) S e t u p
82. Select Start - Programs - Administrative Tools - Internet Authentication Service
83. Right-click on Clients, and select New Client.
Figure 30: Service Screen
84. Enter a name for the access point, click Next.
85. Enter the address or name of the Wireless Access Point, and set the shared secret, as entered on the
Security Settings of the Wireless Access Point.
86. Click Finish.
87. Right-click on Remote Access Policies, select New Remote Access Policy.
88. Assuming you are using EAP-TLS, name the policy eap-tls, and click Next.
89. Click Add...
If you don't want to set any restrictions and a condition is required, select Day-And-Time-Restrictions, and
click Add...
90.
Figure 31: Attribute Screen
91. Click Permitted, then OK. Select Next.
92. Select Grant remote access permission. Click Next.
93. Click Edit Profile... and select the Authentication tab. Enable Extensible Authentication Protocol, and select
Smart Card or other Certificate. Deselect other authentication methods listed. Click OK.
Page 41
P a g e 4 1 o f
9 3
Figure 32: Authentication Screen
94. Select No if you don't want to view the help for EAP. Click Finish.
Page 42
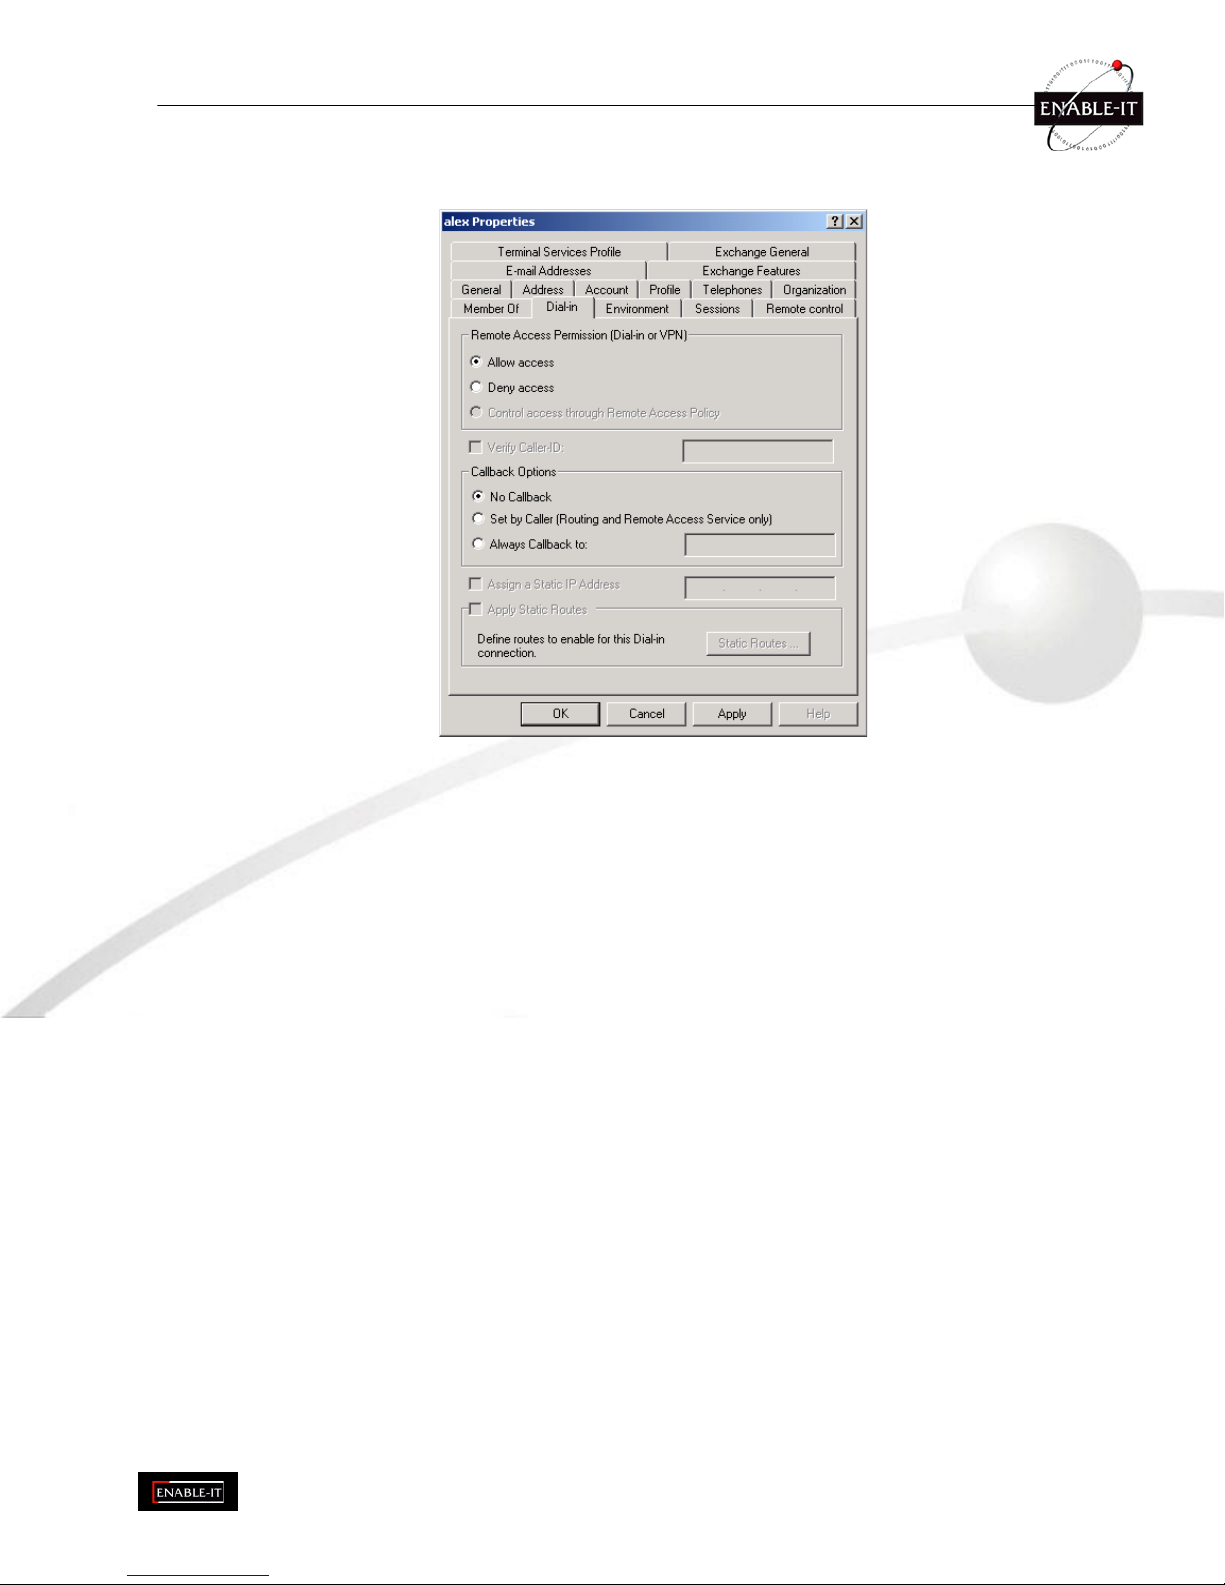
P a g e 4 2 o f
9 3
R e m o t e A c c e s s L o g i n f o r U s e r s
95. Select Start - Programs - Administrative Tools- Active Directory Users and Computers.
96. Double click on the user who you want to enable.
97. Select the Dial-in tab, and enable Allow access. Click OK.
Figure 33: Dial-in Screen
Page 43
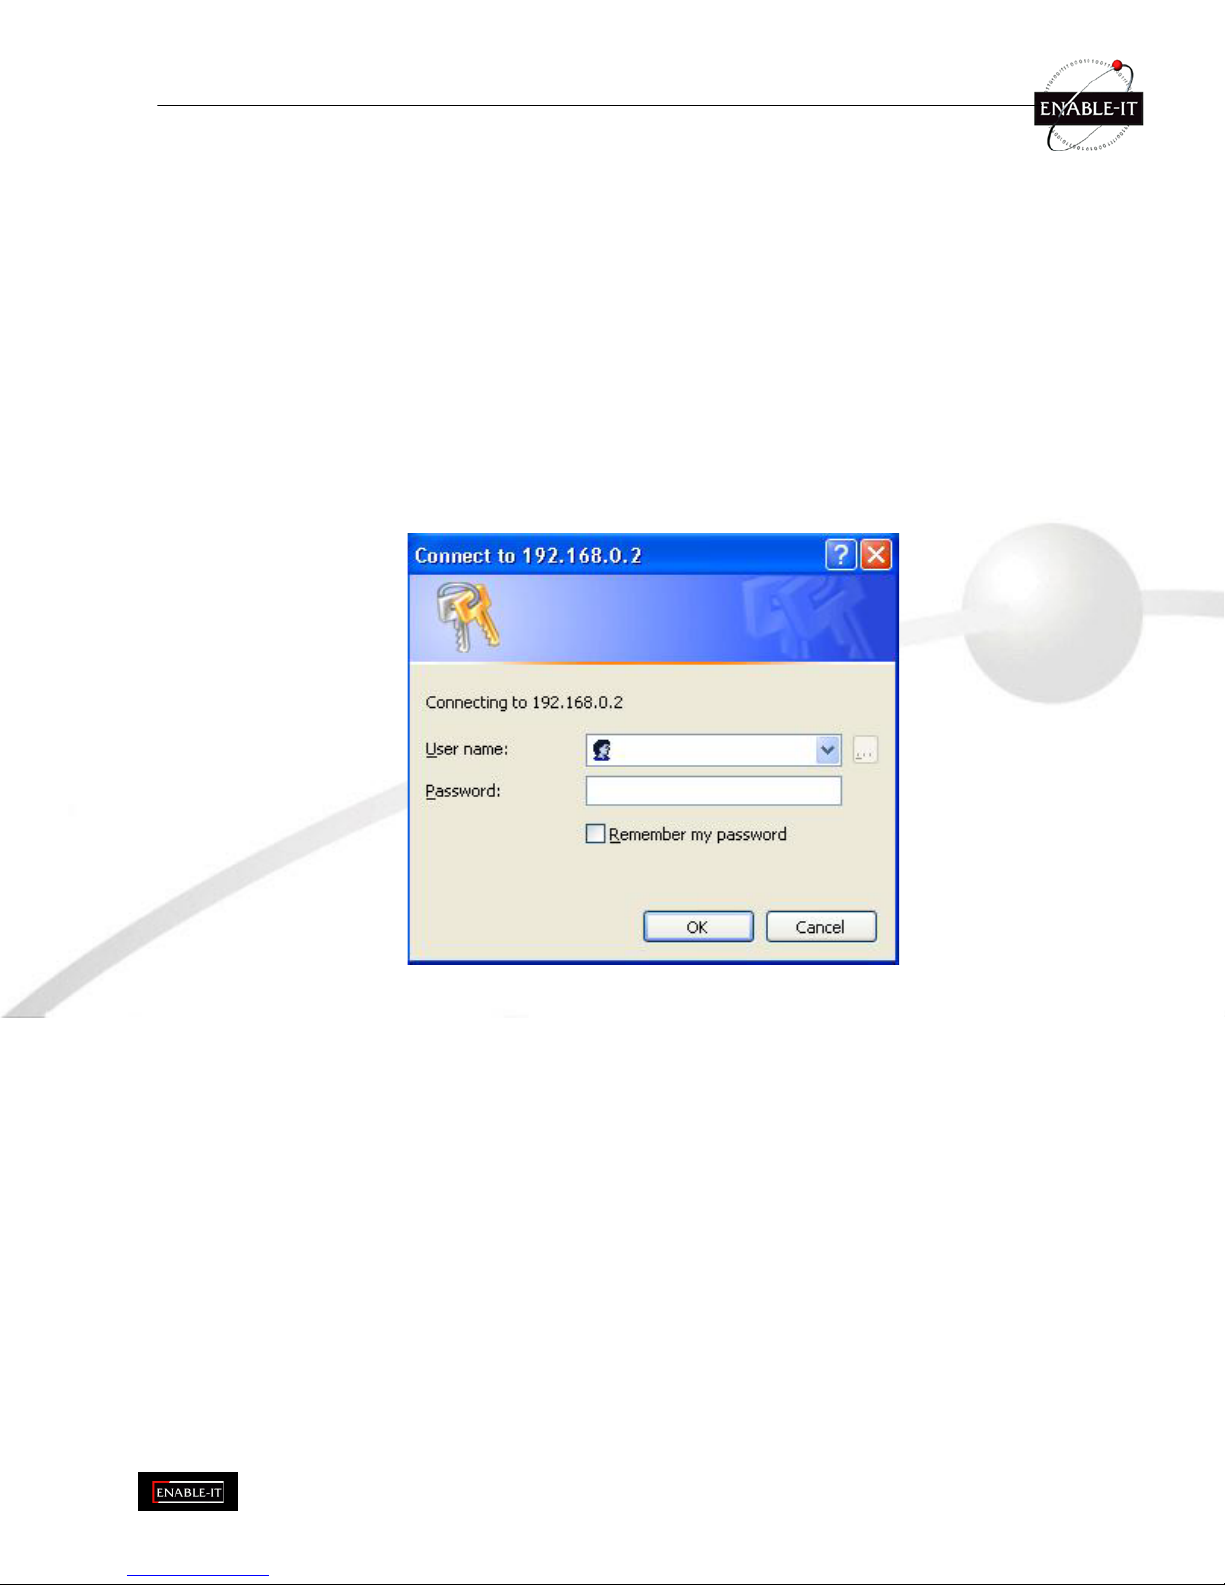
P a g e 4 3 o f
9 3
8 0 2 . 1 x C l i e n t S e t u p o n W i n d o w s X P
W i n d o w s X P s h i p s w i t h a c o m p l e t e 8 0 2 . 1 x c l i e n t i m p l e m e n t a t i o n . I f u s i n g W i n d o w s 2 0 0 0 , y o u c a n i n s t a l l S P 3 ( S e r v i c e
P a c k 3 ) t o g a i n t h e s a m e f u n c t i o n a l i t y .
I f y o u d o n ' t h a v e e i t h e r o f t h e s e s y s t e m s , y o u m u s t u s e t h e 8 0 2 . 1 x c l i e n t s o f t w a r e p r o v i d e d w i t h y o u r w i r e l e s s a d a p t e r .
R e f e r t o y o u r v e n d o r ' s d o c u m e n t a t i o n f o r s e t u p i n s t r u c t i o n s .
T h e f o l l o w i n g i n s t r u c t i o n s a s s u m e t h a t :
• You are using Windows XP
• You are connecting to a Windows 2000 server for authentication.
• You already have a login (User name and password) on the Windows 2000 server.
C l i e n t C e r t i f i c a t e S e t u p
98. Connect to a network which doesn't require port authentication.
99. Start your Web Browser. In the Address box, enter the IP address of the Windows 2000 Server, followed by
/certsrv
e.g
http://192.168.0.2/certsrv
100. You will be prompted for a user name and password. Enter the User name and Password assigned to
you by your network administrator, and click OK.
Figure 34: Connect Screen
101. On the first screen (below), select Request a certificate, click Next.
Page 44
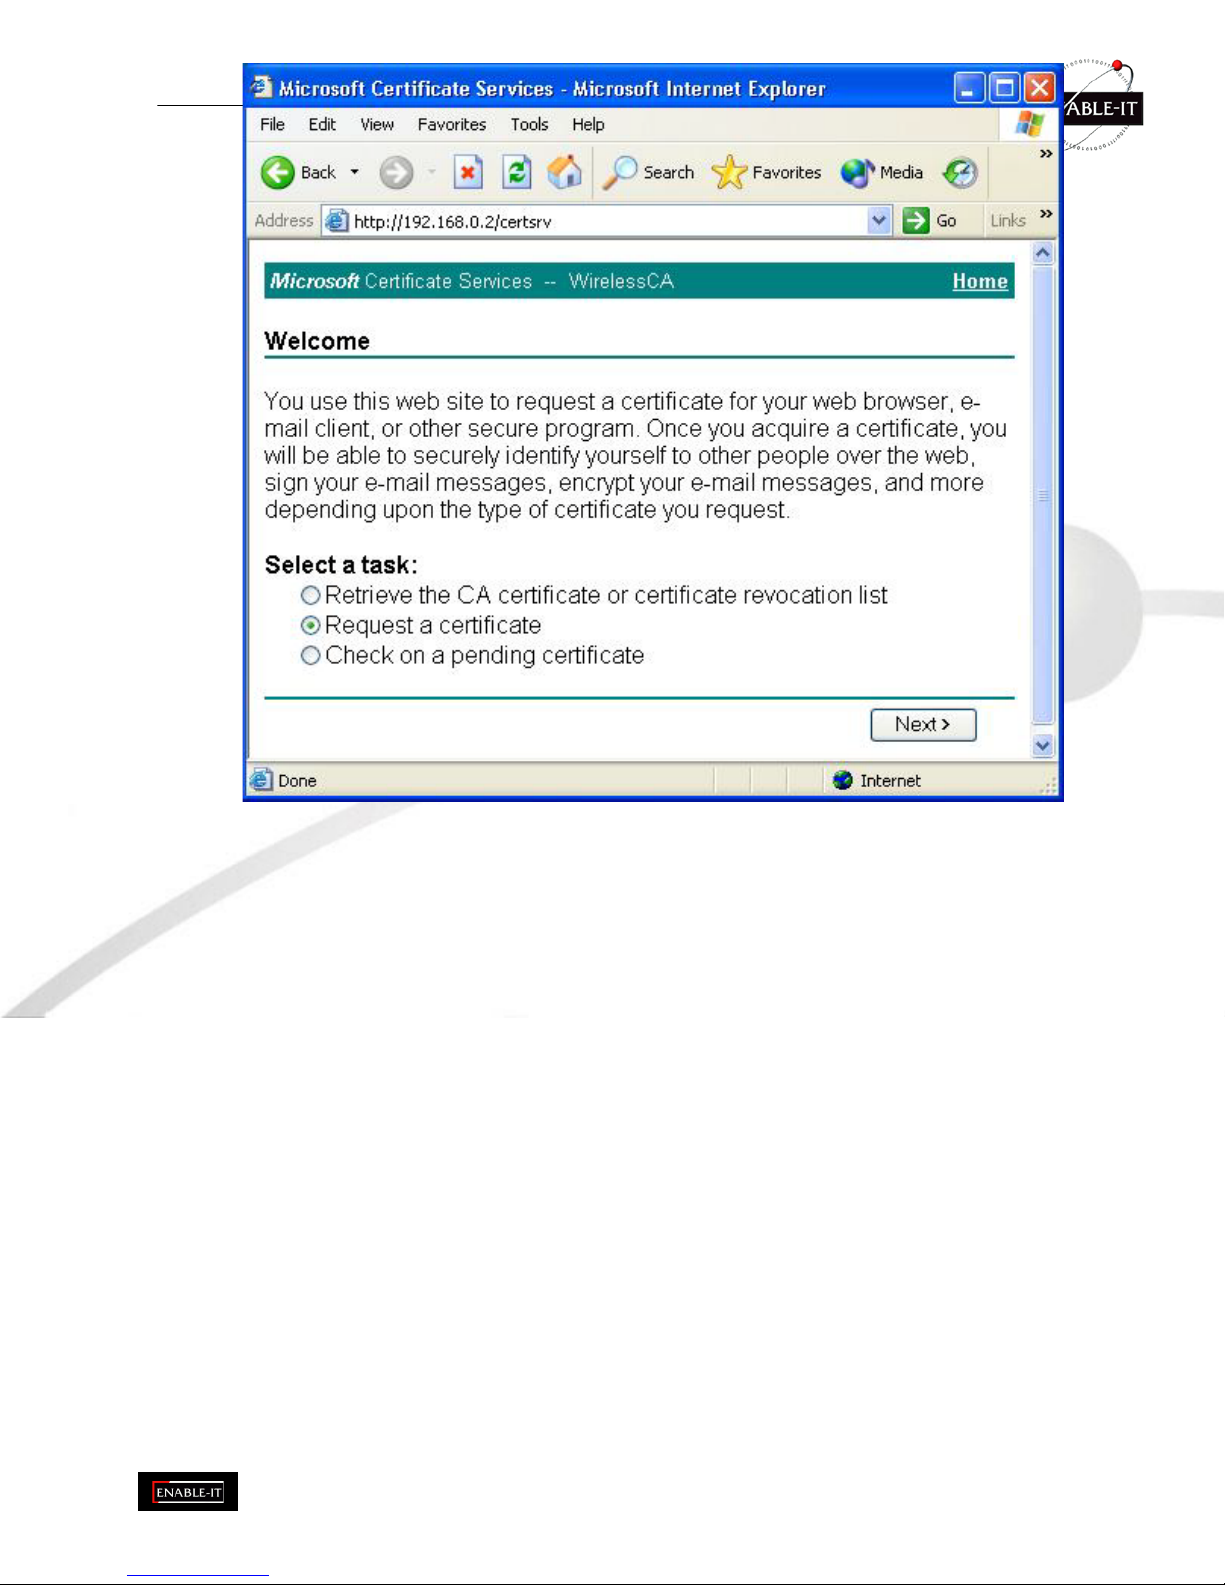
P a g e 4 4 o f
9 3
Figure 35: Wireless CA Screen
102. Select User certificate request and select User Certificate, the click Next.
103.
Page 45
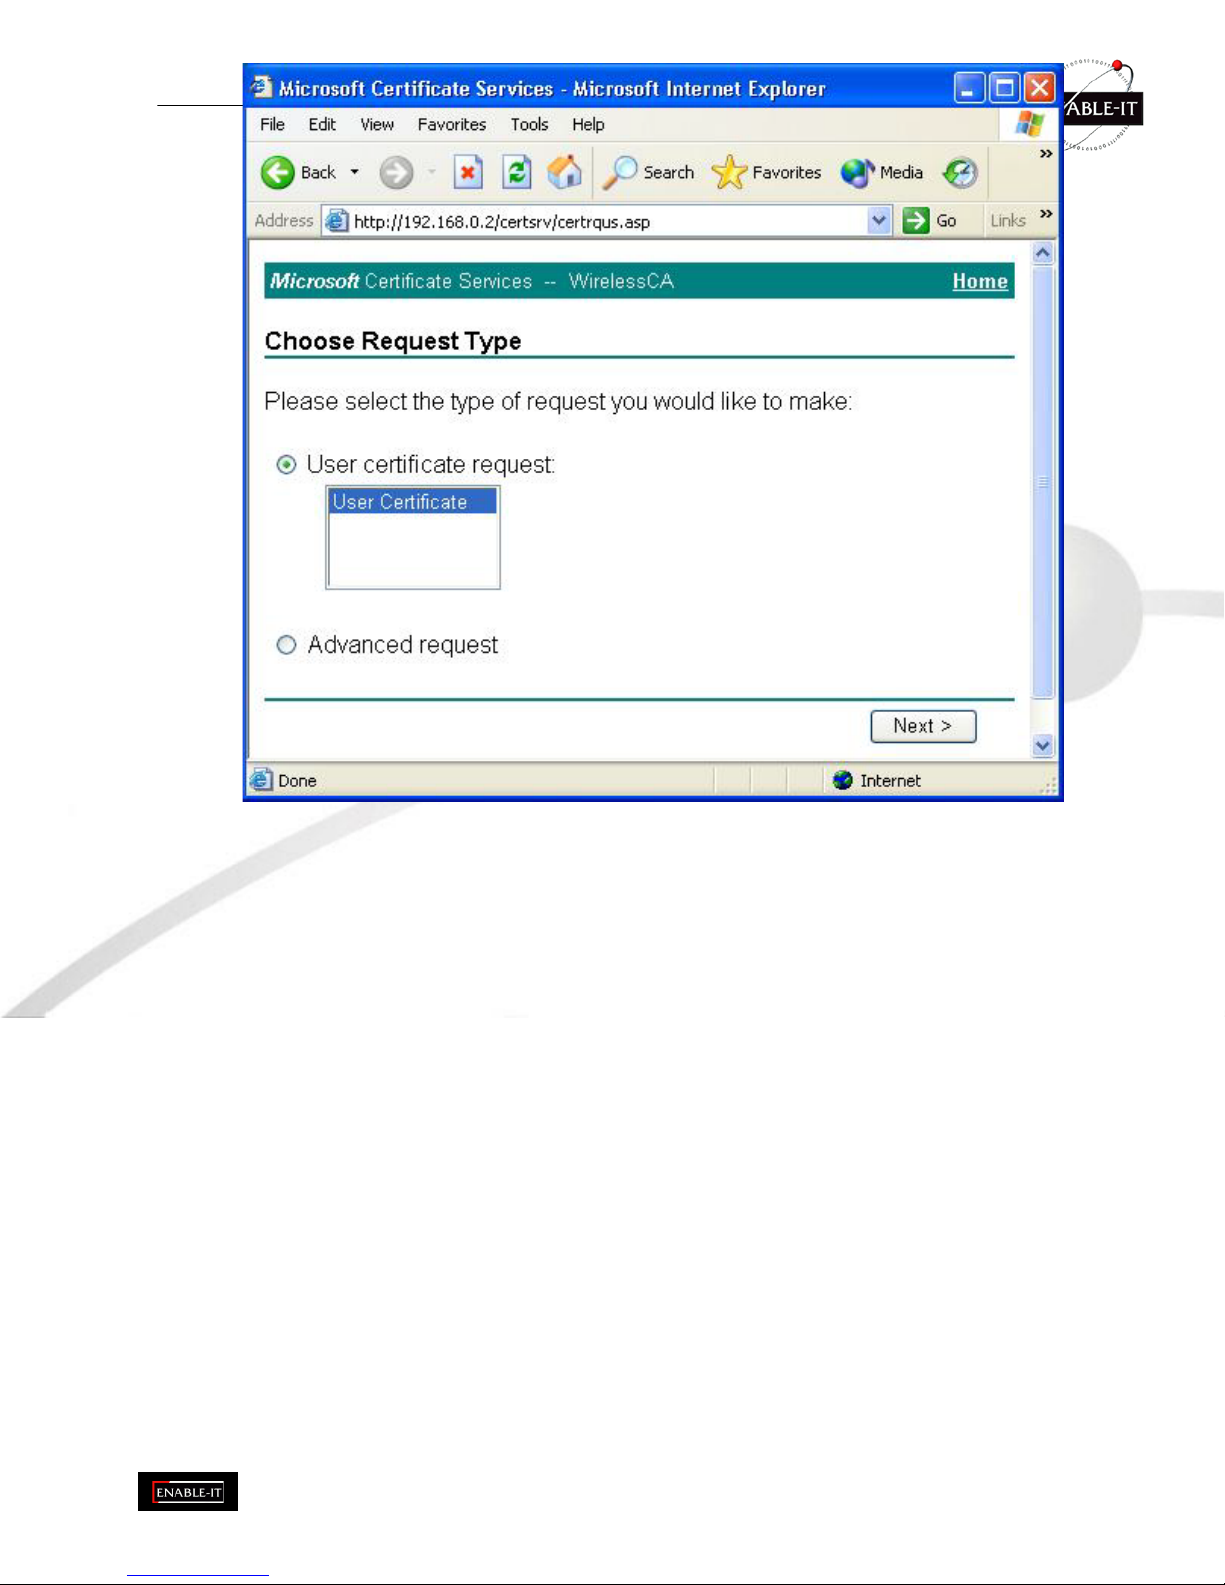
P a g e 4 5 o f
9 3
Figure 36: Request Type Screen
104. Click Submit.
Page 46
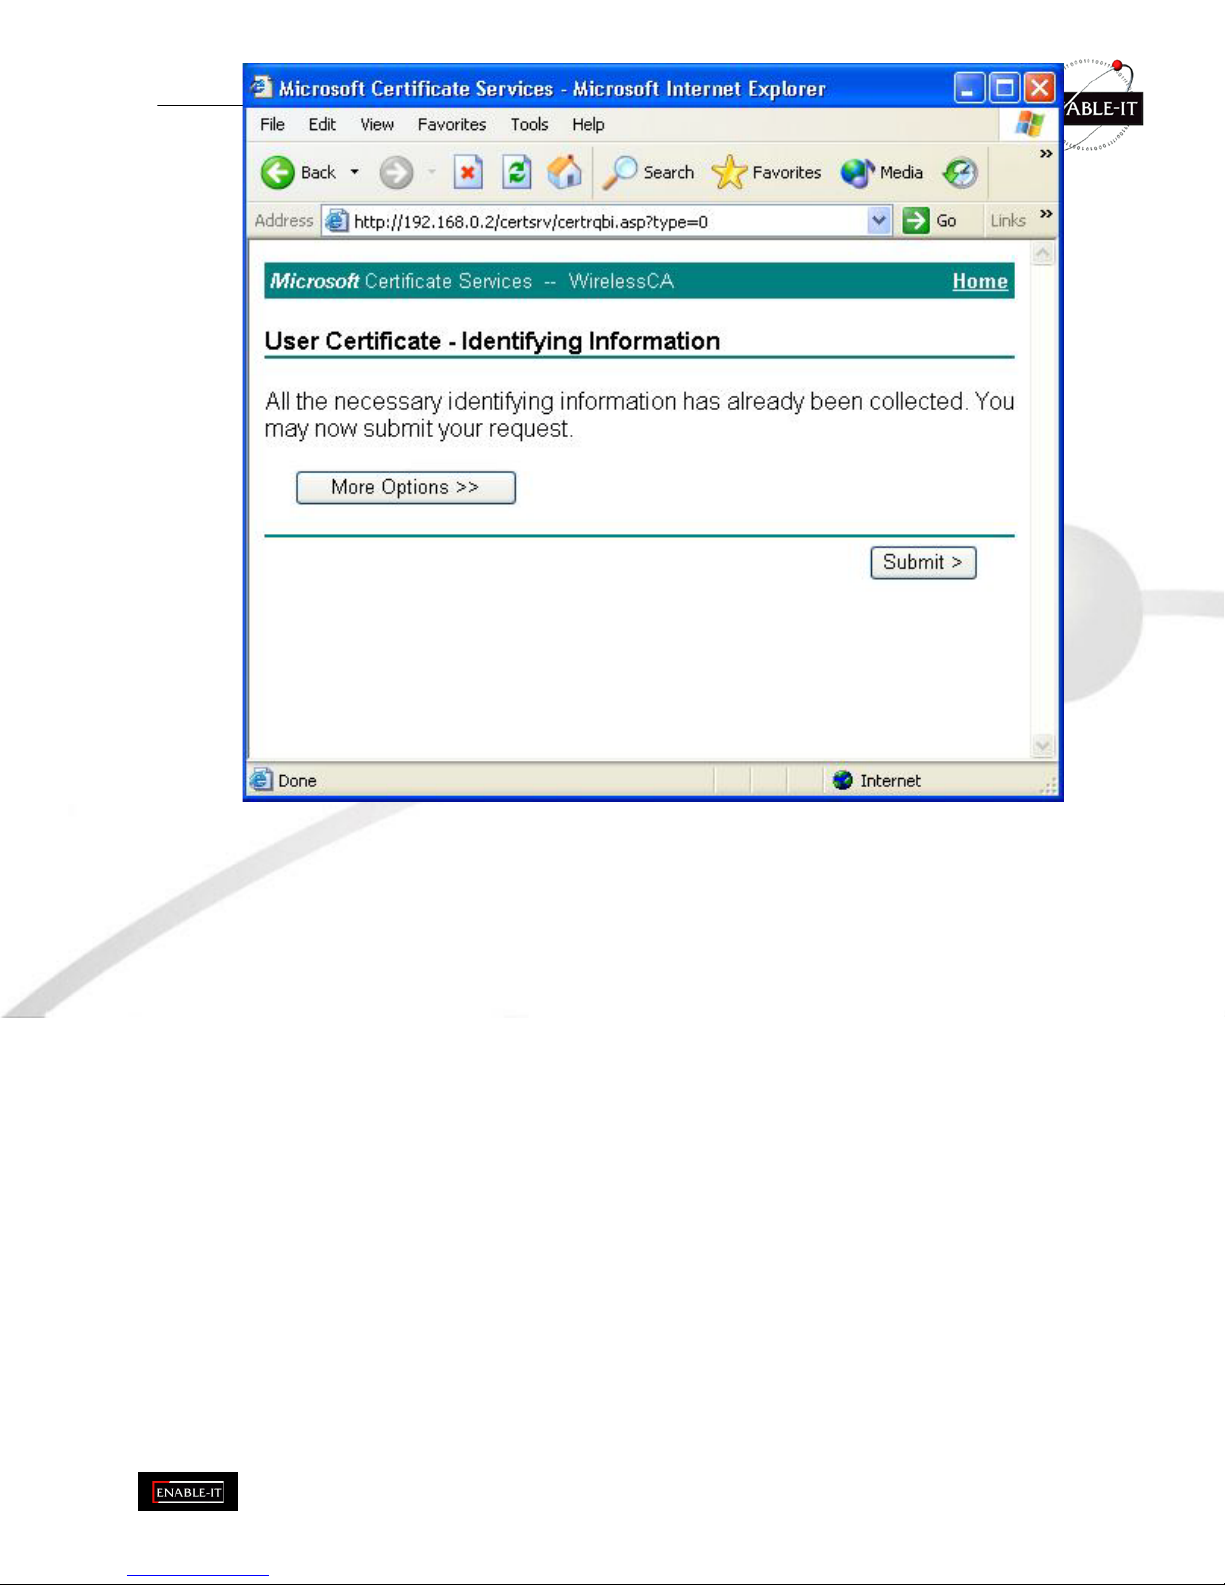
P a g e 4 6 o f
9 3
Figure 37: Identifying Information Screen
105. A message will be displayed, then the certificate will be returned to you.
Click Install this certificate.
Page 47
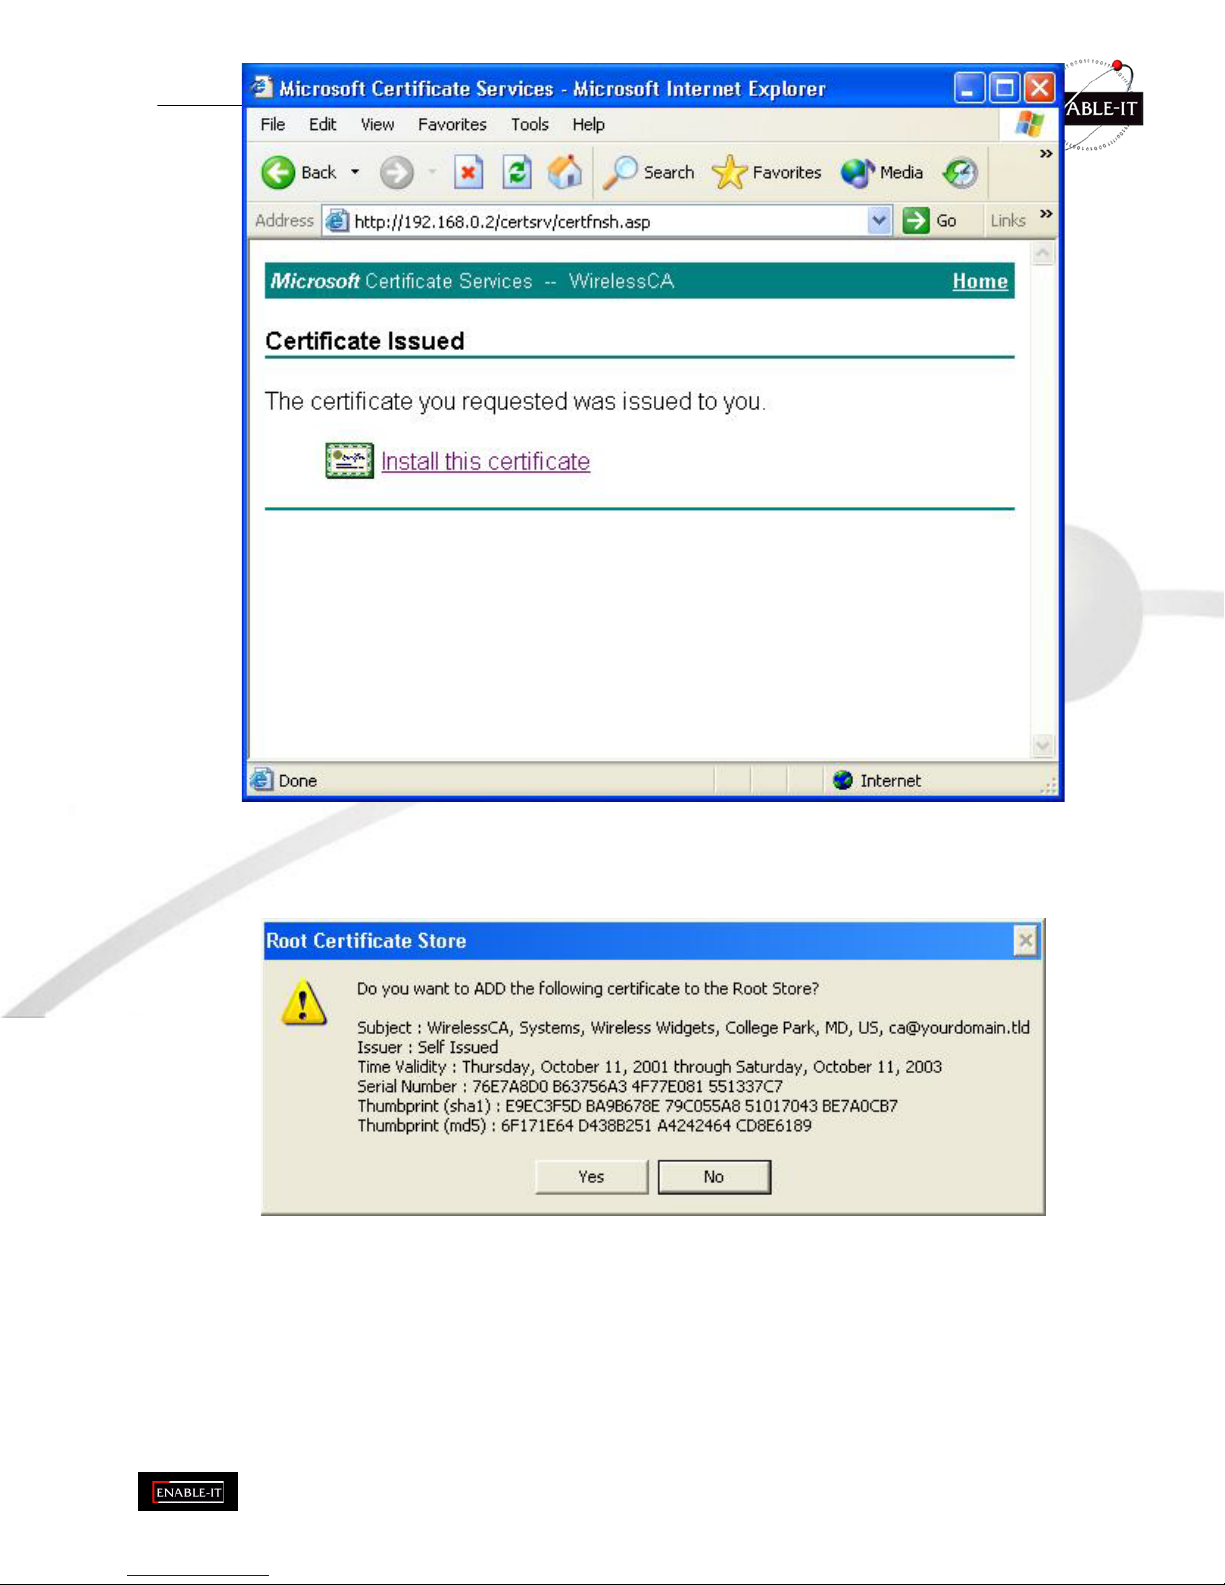
P a g e 4 7 o f
9 3
Figure 38:Certificate Issued Screen
106. . You will receive a confirmation message. Click Yes.
Figure 39: Root Certificate Screen
107. Certificate setup is now complete.
8 0 2 . 1 x A u t h e n t i c a t i o n S e t u p
108. Open the properties for the wireless connection, by selecting Start - Control Panel - Network
Connections.
109. Right Click on the Wireless Network Connection, and select Properties.
Page 48
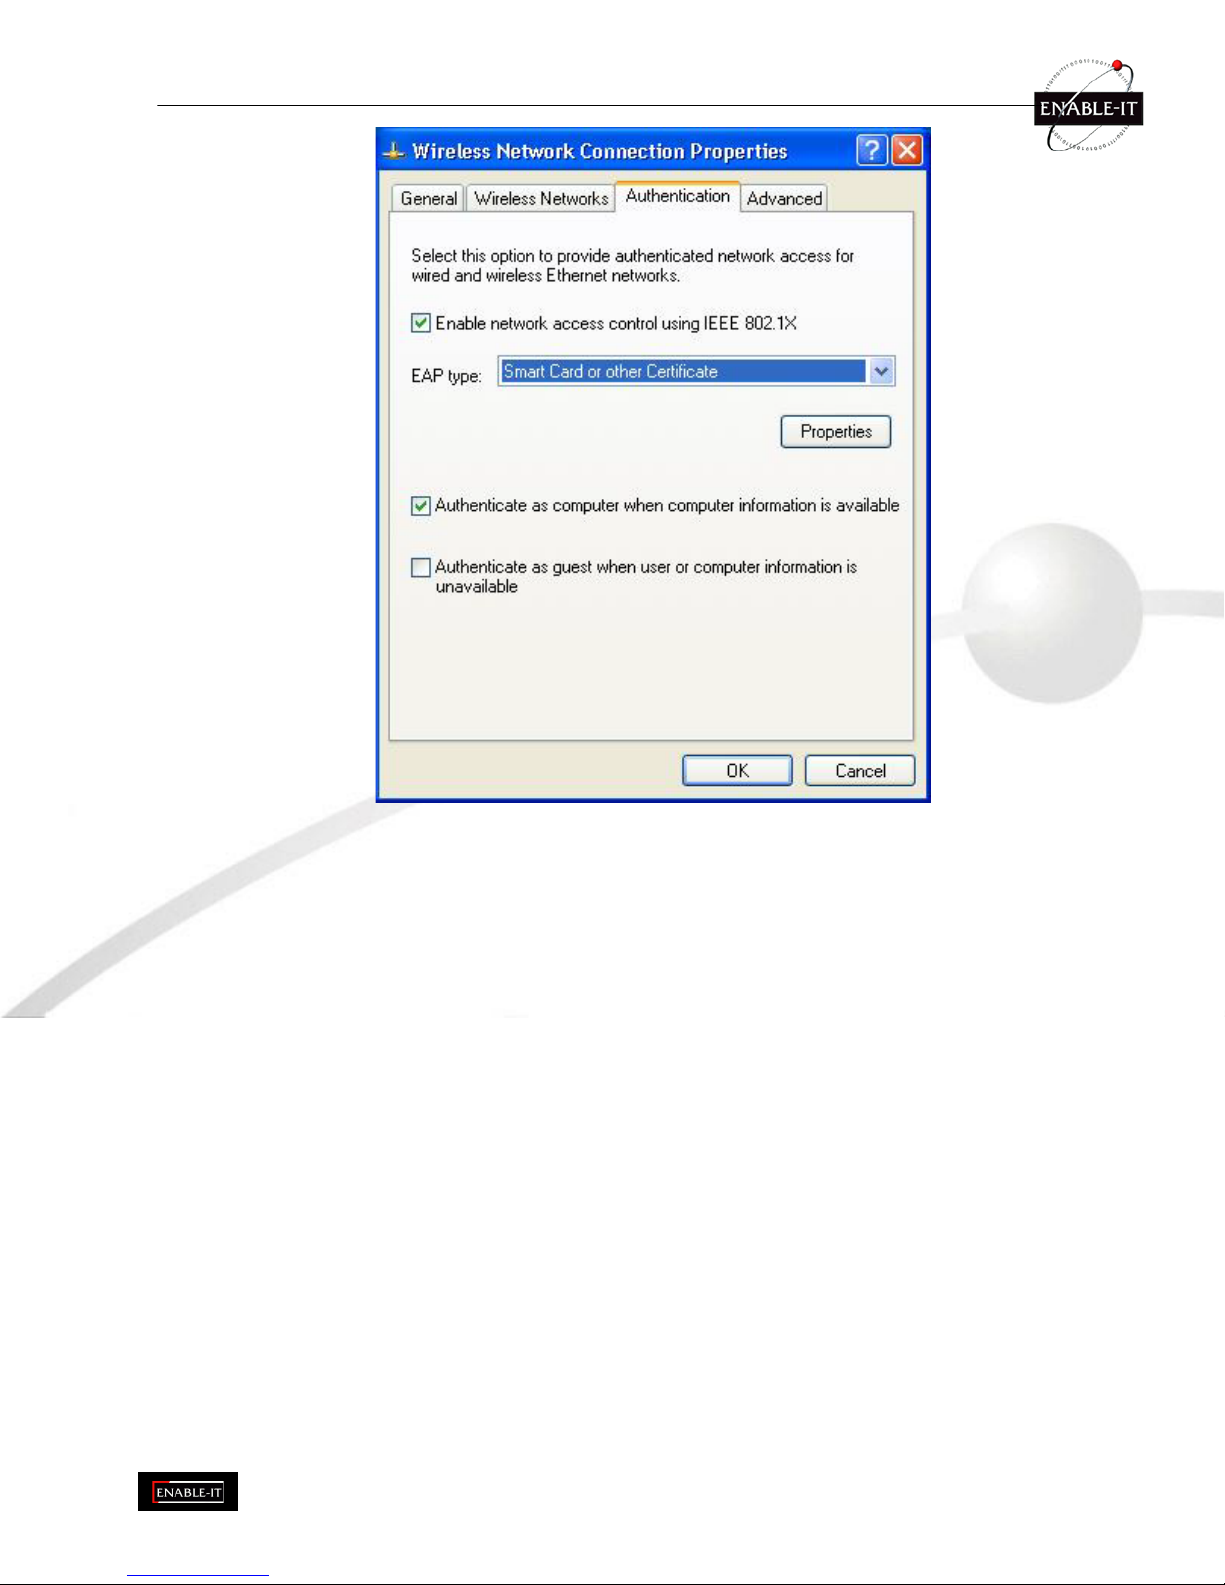
P a g e 4 8 o f
9 3
110. Select the Authentication Tab, and ensure that Enable network access control using IEEE 802.1X is
selected, and Smart Card or other Certificate is selected from the EAP type.
Figure 40: Authentication Tab
E n c r y p t i o n S e t t i n g s
T h e E n c r y p t i o n s e t t i n g s m u s t m a t c h t h e A P s ( A c c e s s P o i n t s ) o n t h e W i r e l e s s n e t w o r k y o u w i s h t o j o i n .
• Windows XP will detect any available Wireless networks, and allow you to configure each network
independently.
• Your network administrator can advise you of the correct settings for each network. 802.1x networks typically
use EAP-TLS. This is a dynamic key system, so there is no need to enter key values.
E n a b l i n g E n c r y p t i o n
T o e n a b l e e n c r y p t i o n f o r a w i r e l e s s n e t w o r k , f o l l o w t h i s p r o c e d u r e :
111. Click on the Wireless Networks tab.
Page 49
P a g e 4 9 o f
9 3
Figure 41: Wireless Networks Screen
112. Select the wireless network from the Available Networks list, and click Configure.
113. Select and enter the correct values, as advised by your Network Administrator.
For example, to use EAP-TLS, you would enable Data encryption, and click the checkbox for the setting The
key is provided for me automatically, as shown below.
Page 50
P a g e 5 0 o f
9 3
Figure 42: Properties Screen
S e t u p f o r W i n d o w s X P a n d 8 0 2 . 1 x c l i e n t i s n o w c o m p l e t e .
Page 51
P a g e 5 1 o f
9 3
U s i n g 8 0 2 . 1 x M o d e ( w i t h o u t W P A )
T h i s i s v e r y s i m i l a r t o u s i n g W P A -8 0 2 . 1 x .
T h e o n l y d i f f e r e n c e i s t h a t o n y o u r c l i e n t , y o u m u s t N O T e n a b l e t h e s e t t i n g T h e k e y i s p r ov i d e d f o r m e a u t o m a t i c a l l y .
I n s t e a d , y o u m u s t e n t e r t h e W E P k e y m a n u a l l y , e n s u r i n g i t m a t c h e s t h e W E P k e y u s e d o n t h e A c c e s s P o i n t .
Figure 43: Properties Screen
Page 52
P a g e 5 2 o f
9 3
U s i n g W P A -P S K
F o r e a c h o f t h e f o l l o w i n g i t e m s , e a c h W i r e l e s s S t a t i o n m u s t h a v e t h e s a m e s e t t i n g s a s t h e W i r e l e s s A c c e s s P o i n t .
M o d e
O n e a c h P C , t h e m o d e m u s t b e s e t t o I n f r a s t r u ct u r e .
S S I D ( E S S I D )
T h i s m u s t m a t c h t h e v a l u e u s e d o n t h e W i r e l e s s A c c e s s P o i n t .
T h e d e f a u l t v a l u e i s w i r e l e s s
N o t e ! T h e S S I D i s c a s e s e n s i t i v e .
W i r e l e s s
S e c u r i t y
O n e a c h c l i e n t , W i r e l e s s s e c u r i t y m u s t b e s e t t o W P A -P S K .
• The Pre-shared Key entered on the Access Point must also
be entered on each Wireless client.
• The Encryption method (e.g. TKIP, AES) must be set to
match the Access Point.
Page 53
P a g e 5 3 o f
9 3
U s i n g W P A -8 0 2 . 1 x
Th i s i s t h e m o s t s e c u r e a n d m o s t c o m p l e x s y s t e m .
8 0 2 . 1 x m o d e p r o v i d e s g r e a t e r s e c u r i t y a n d c e n t r a l i z e d m a n a g e m e n t , b u t i t i s m o r e c o m p l e x t o c o n f i g u r e .
Wireless Station Configuration
F o r e a c h o f t h e f o l l o w i n g i t e m s , e a c h W i r e l e s s S t a t i o n m u s t h a v e t h e s a m e s e t t i n g s a s t h e W i r e l e s s A c c e s s P o i n t .
M o d e
O n e a c h P C , t h e m o d e m u s t b e s e t t o I n f r a s t r u ct u r e .
S S I D ( E S S I D )
T h i s m u s t m a t c h t h e v a l u e u s e d o n t h e W i r e l e s s A c c e s s P o i n t .
T h e d e f a u l t v a l u e i s w i r e l e s s
N o t e ! T h e S S I D i s c a s e s e n s i t i v e .
8 0 2 . 1 x
A u t h e nt i c at i o n
E a c h c l i e n t m u s t o b t a i n a C e r t i f i c a t e w h i c h i s u s e d f o r a u t h e n t i c at i o n
f o r t h e R a d i u s S e r v e r .
8 0 2 . 1 x
E n c r y p t i o n
T y p i c a l l y , E A P -T L S i s u s e d . T h i s i s a d y n a m i c k e y s y s t e m , s o k e y s d o
N O T h a v e t o b e e n t e r e d o n e a c h W i r e l e s s s t a t i o n .
H o w e v e r , y o u c a n a l s o u s e a s t a t i c W E P k e y ( E A P -M D 5 ) ; t h e
W i r e l e s s A c c e s s P o i n t s u p p o r t s b o t h m e t h o d s s i m u l t a n e o u s l y .
Radius Server Configuration
I f u s i n g W P A -8 0 2 . 1 x m o d e , t h e R a d i u s S e r v e r o n y o u r n e t w o r k m u s t b e c o n f i g u r e d a s f o l l o w :
• It must provide and accept Certificates for user authentication.
• There must be a Client Login for the Wireless Access Point itself.
• The Wireless Access Point will use its Default Name as its Client Login name. (However, your Radius
server may ignore this and use the IP address instead.)
• The Shared Key, set on the Security Screen of the Access Point, must match the Shared Secret value on
the Radius Server.
• Encryption settings must be correct.
Page 54
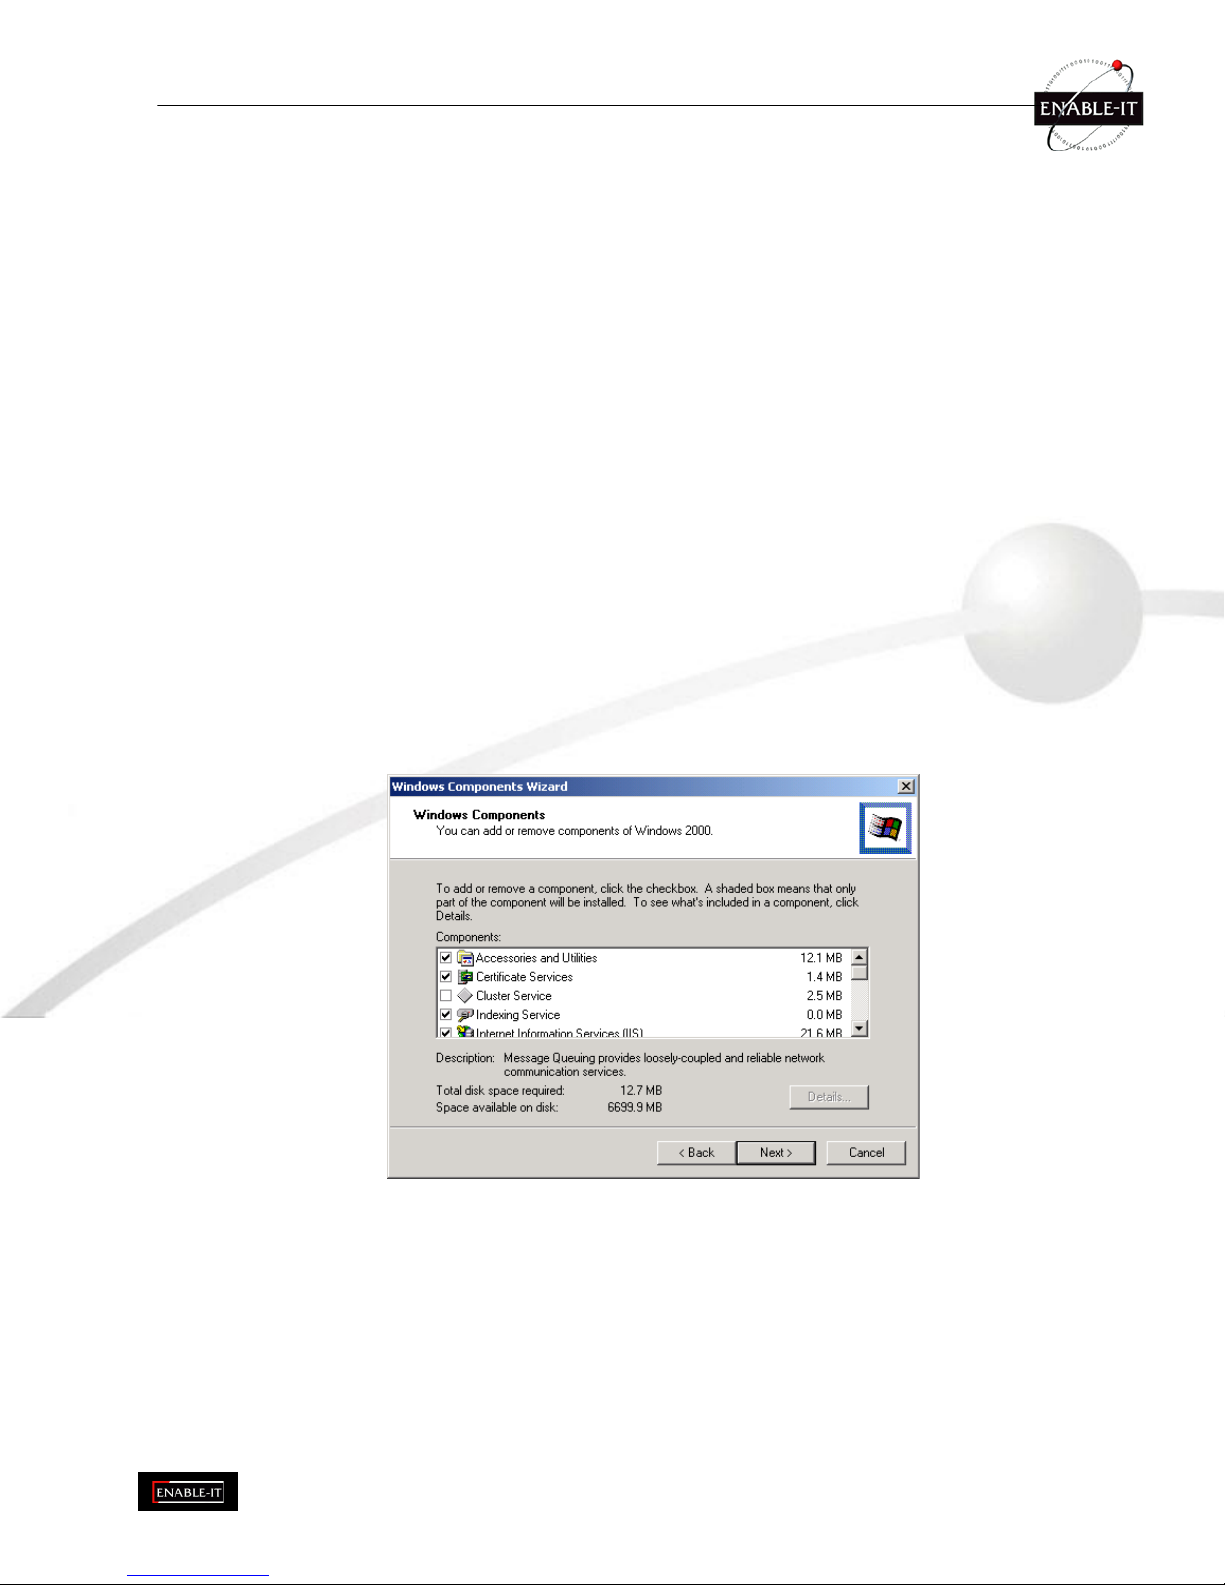
P a g e 5 4 o f
9 3
8 0 2 . 1 x S e r v e r S e t u p ( W i n d o w s 2 0 0 0 S e r v e r )
T h i s s e c t i o n d e s c r i b e s u s i n g M i c r o s o f t I n t e r n e t A u t h e n t i c a t i o n S e r v e r a s t h e R a d i u s S e r v e r , s i n c e i t i s t h e m o s t c o m m o n
R a d i u s S e r v e r a v a i l a b l e t h a t s u p p o r t s t h e E A P -T L S a u t h e n t i c a t i o n m e t h o d .
T h e f o l l o w i n g s e r v i c e s o n t h e W i n d o w s 2 0 0 0 D o m a i n C o n t r o l l e r ( P D C ) a r e a l s o r eq u i r e d :
• dhcpd
• dns
• rras
• webserver (IIS)
• Radius Server (Internet Authentication Service)
• Certificate Authority
W i n d o w s 2 0 0 0 D o m a i n C o n t r o l l e r S e t u p
114. Run dcpromo.exe from the command prompt.
115. Follow all of the default prompts, ensure that DNS is installed and enabled during installation.
S e r v i c e s I n s t a l l a t i o n
116. Select the Control Panel - Add/Remove Programs.
117. Click Add/Remove Windows Components from the left side.
118. Ensure that the following components are activated (selected):
• Certificate Services. After enabling this, you will see a warning that the computer cannot be renamed and
joined after installing certificate services. Select Yes to select certificate services and continue
• World Wide Web Server. Select World Wide Web Server on the Internet Information Services (IIS)
component.
• From the Networking Services category, select Dynamic Host Configuration Protocol (DHCP), and
Internet Authentication Service (DNS should already be selected and installed).
Figure 44: Components Screen
119. Click Next.
120. Select the Enterprise root CA, and click Next.
Page 55
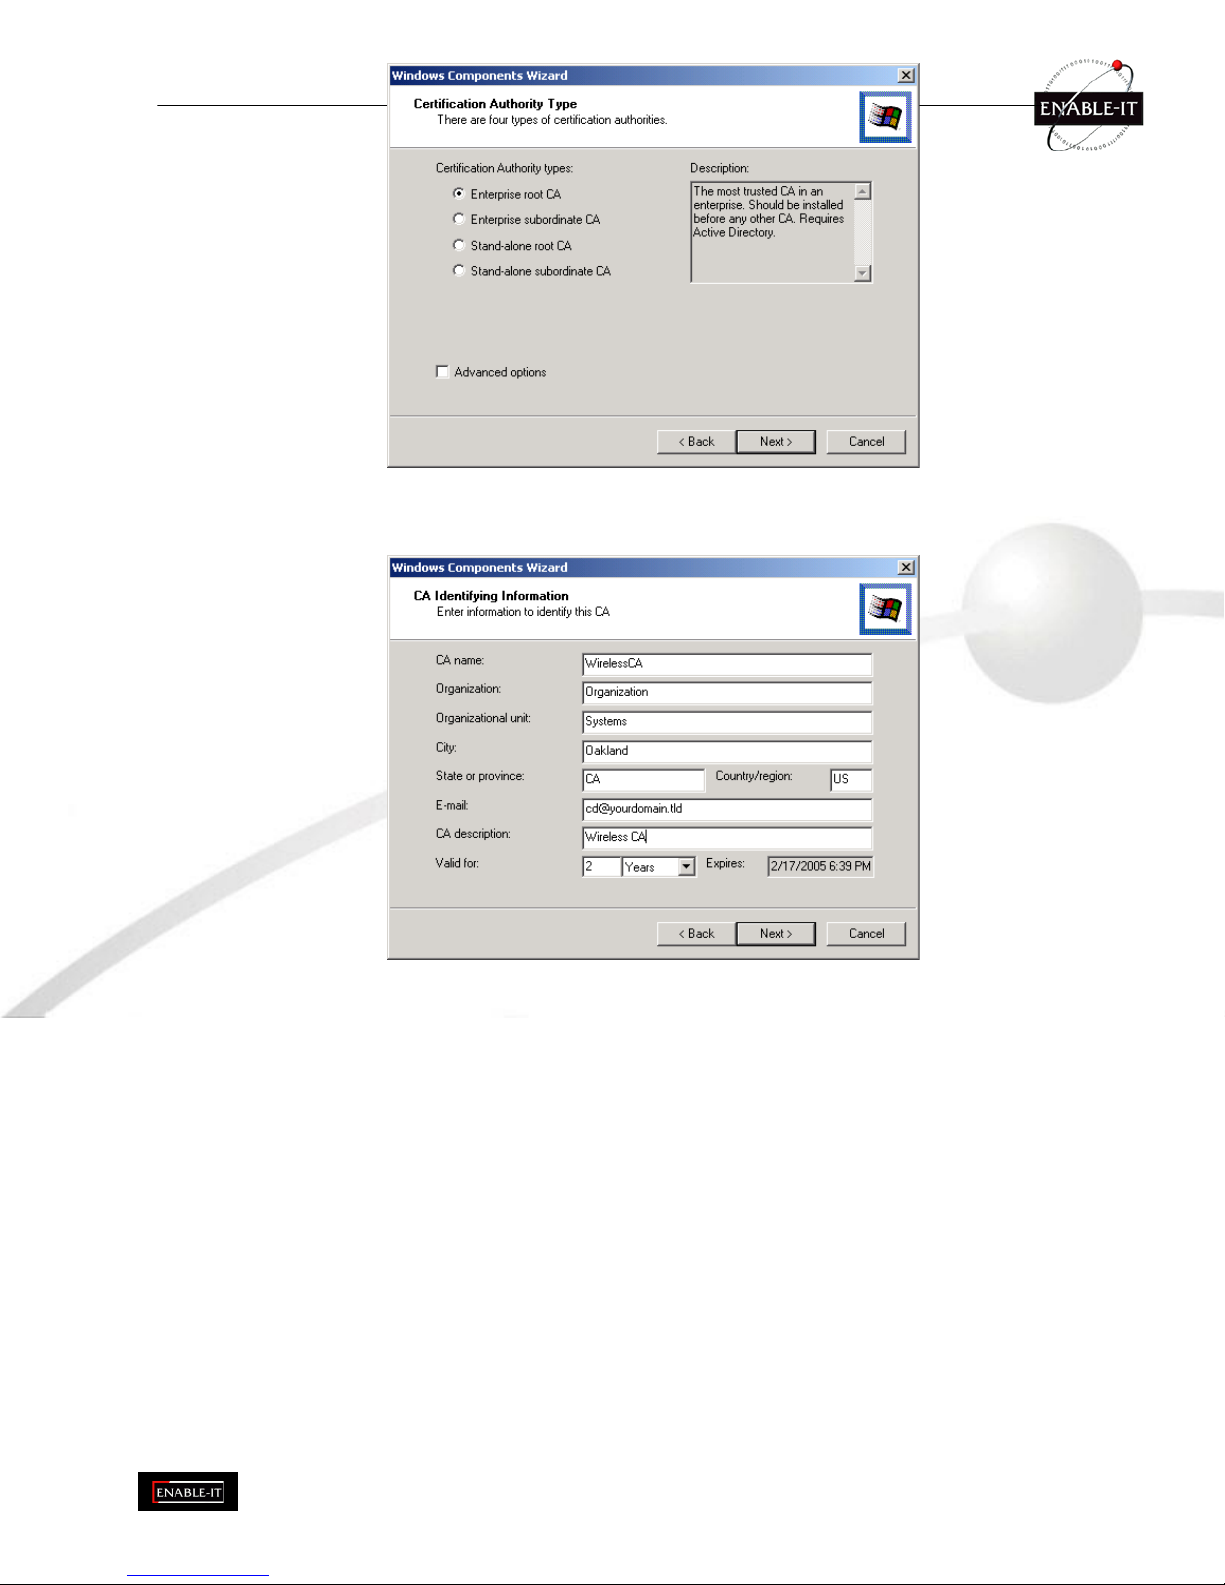
P a g e 5 5 o f
9 3
Figure 45: Certification Screen
121. Enter the information for the Certificate Authority, and click Next.
Figure 46: CA Screen
122. Click Next if you don't want to change the CA's configuration data.
123. Installation will warn you that Internet Information Services are running, and must be stopped before
continuing. Click Ok, then Finish.
D H C P s e r v e r c o n f i g u r a t i o n
124. Click on the Start - Programs - Administrative Tools - DHCP
125. Right-click on the server entry as shown, and select New Scope.
Page 56
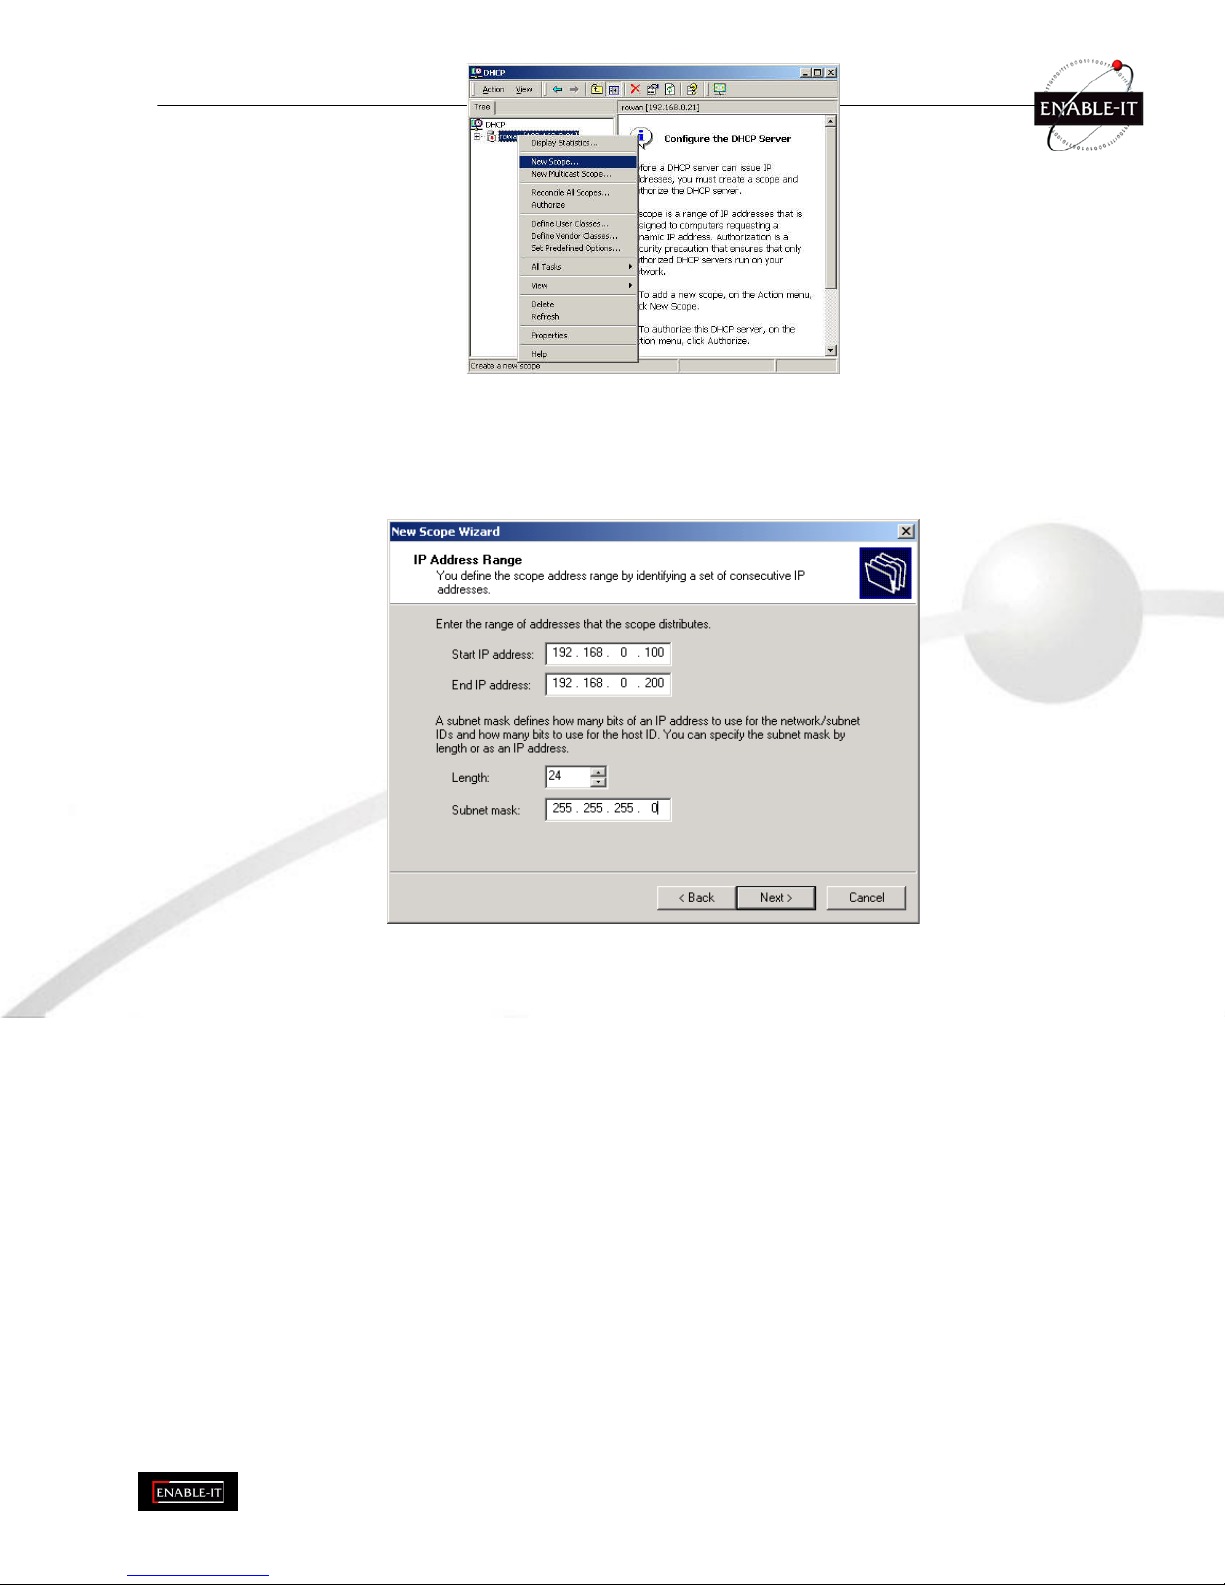
P a g e 5 6 o f
9 3
Figure 47: DHCP Screen
126. Click Next when the New Scope Wizard Begins.
127. Enter the name and description for the scope, click Next.
128. Define the IP address range. Change the subnet mask if necessary. Click Next.
Figure 48:IP Address Screen
129. Add exclusions in the address fields if required. If no exclusions are required, leave it blank. Click Next.
130. Change the Lease Duration time if preferred. Click Next.
131. Select Yes, I want to configure these options now, and click Next.
132. Enter the router address for the current subnet. The router address may be left blank if there is no router.
Click Next.
133. For the Parent domain, enter the domain you specified for the domain controller setup, and enter the
server's address for the IP address. Click Next.
Page 57
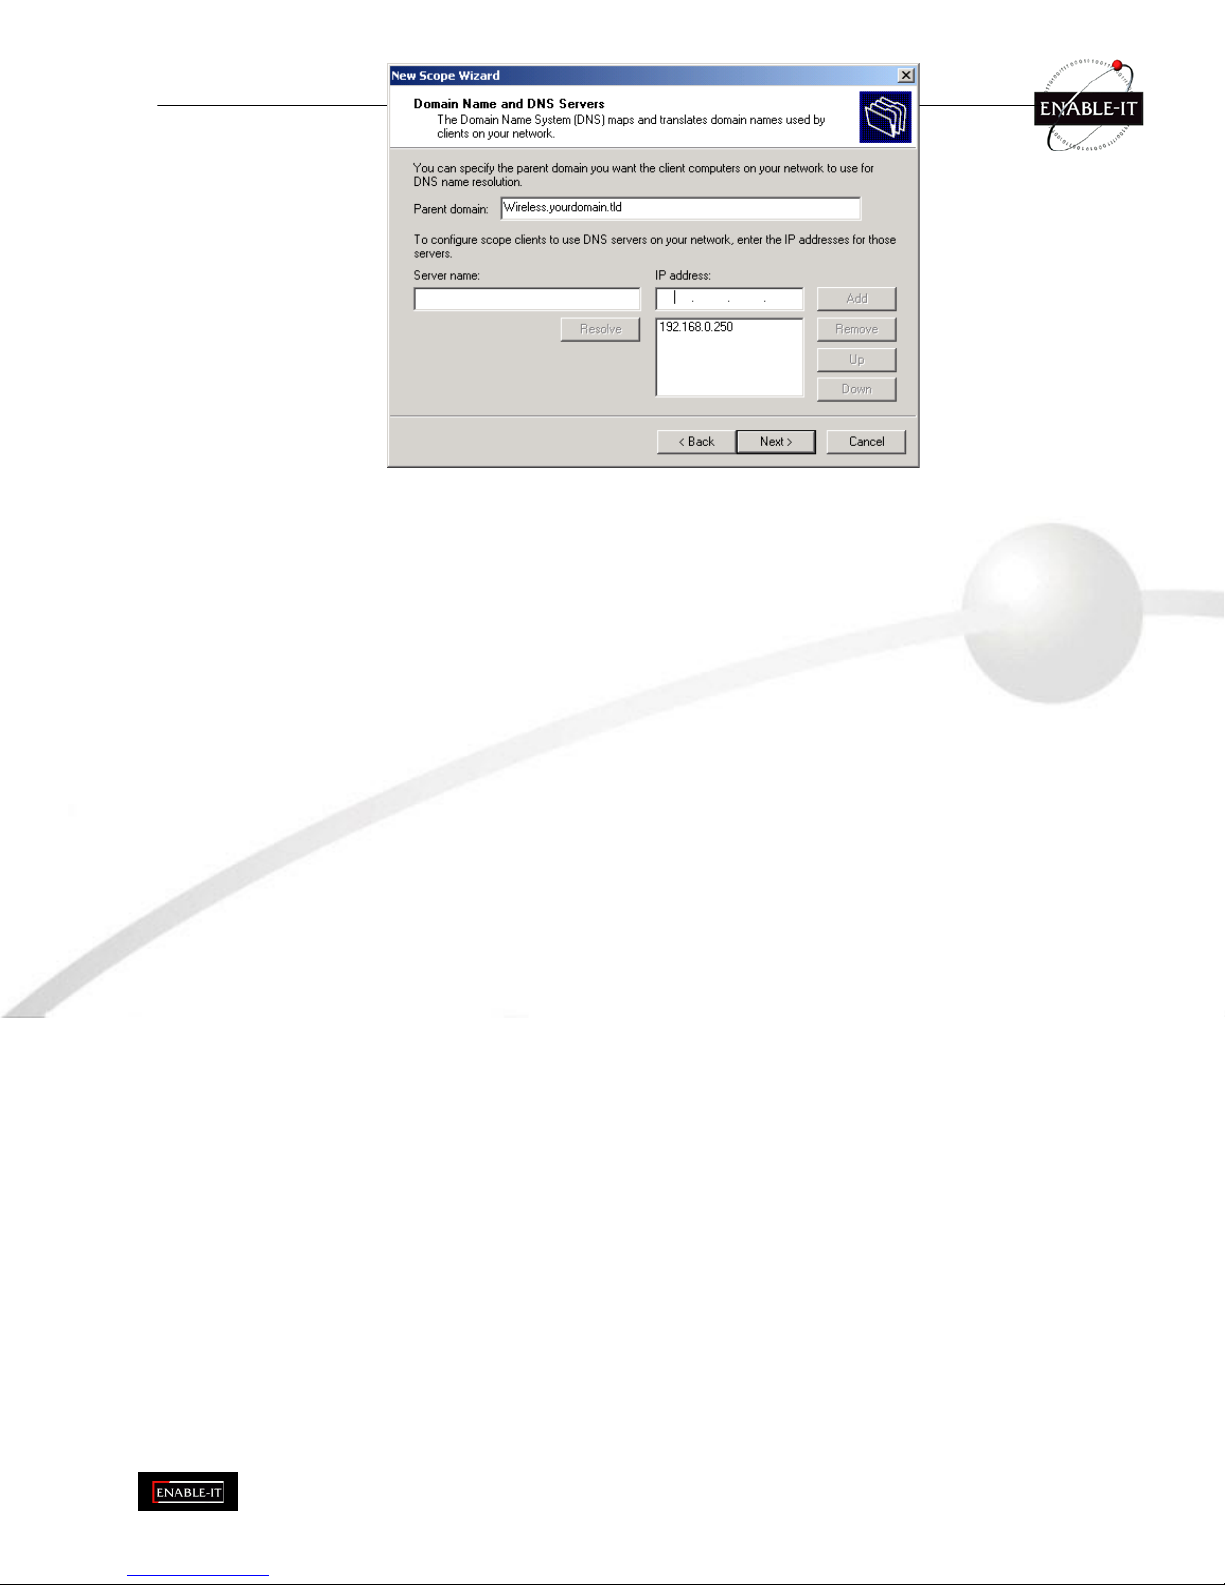
P a g e 5 7 o f
9 3
Figure 49: DNS Screen
134. If you don't want a WINS server, just click Next.
135. Select Yes, I want to activate this scope now. Click Next, then Finish.
136. Right-click on the server, and select Authorize. It may take a few minutes to complete.
Page 58
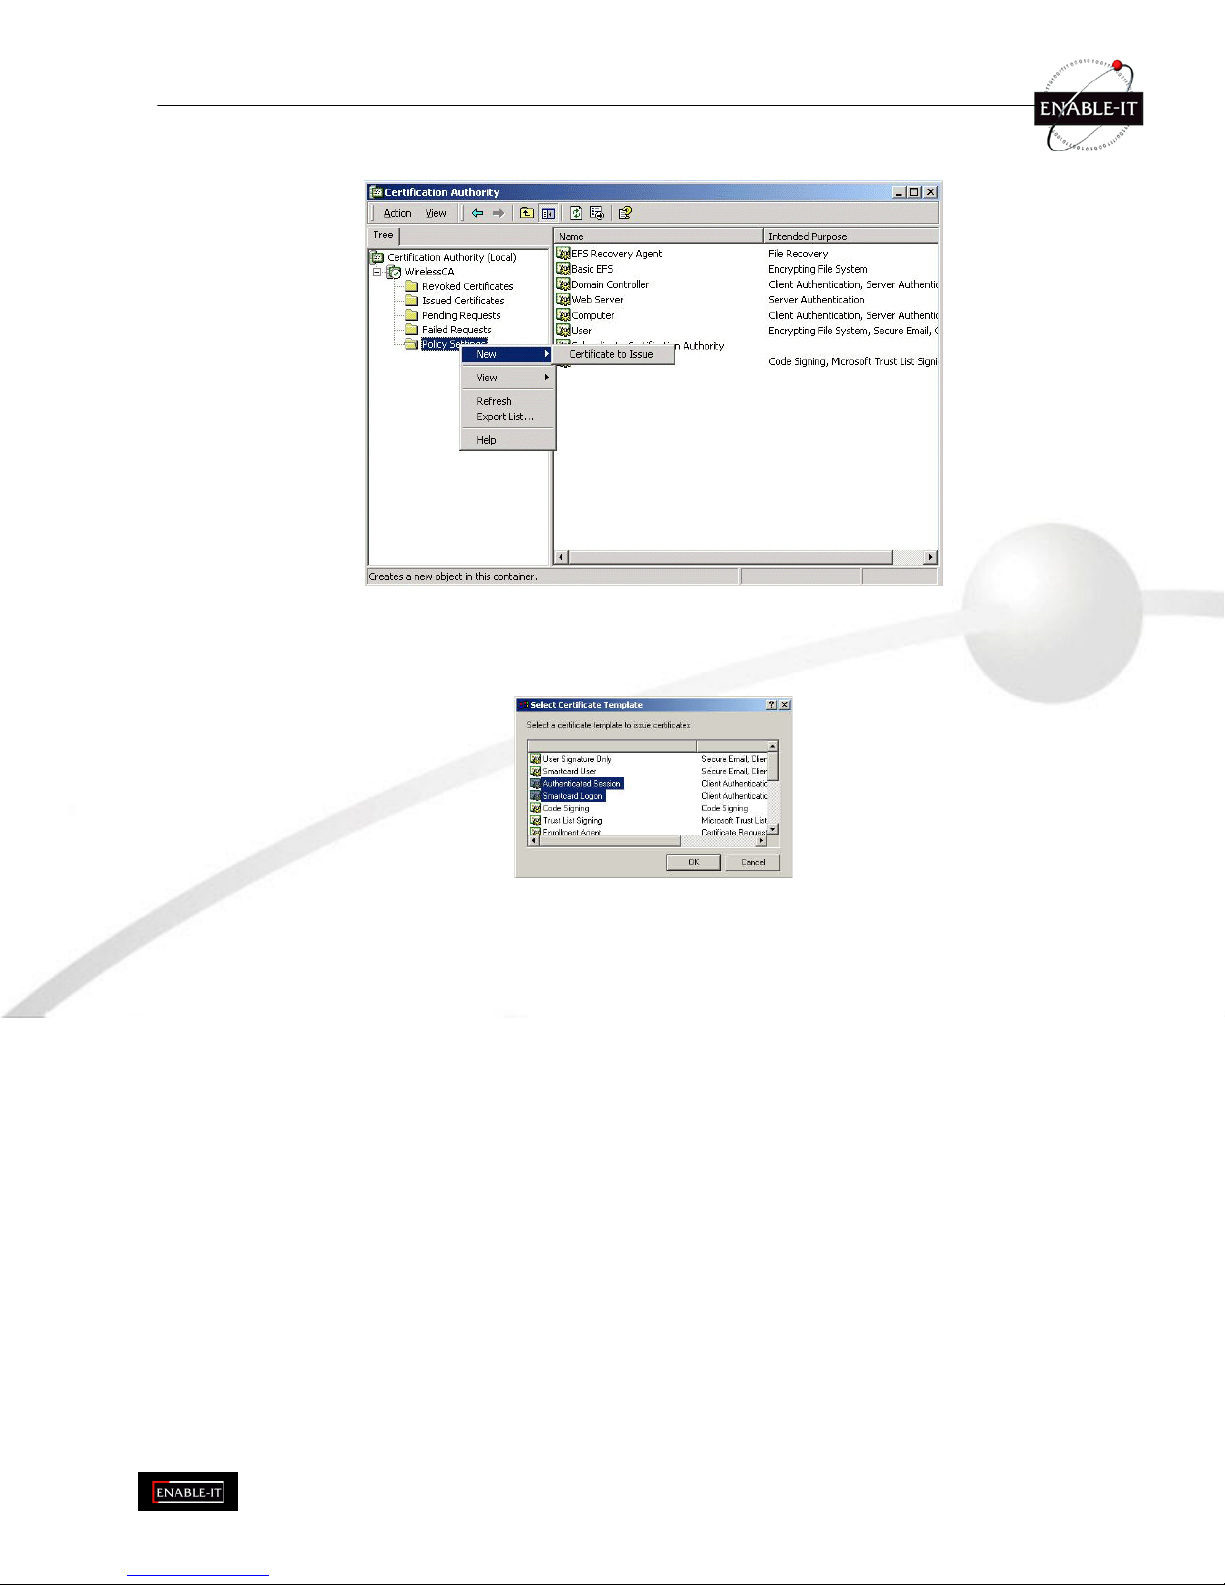
P a g e 5 8 o f
9 3
C e r t i f i c a t e A u t h o r i t y S e t u p
137. Select Start - Programs - Administrative Tools - Certification Authority.
138. Right-click Policy Settings, and select New - Certificate to Issue.
Figure 50: Certificate Authority Screen
139. Select Authenticated Session and Smartcard Logon (select more than one by holding down the Ctrl key).
Click OK.
Figure 51: Template Screen
140. Select Start - Programs - Administrative Tools - Active Directory Users and Computers.
141. Right-click on your active directory domain, and select Properties.
Page 59
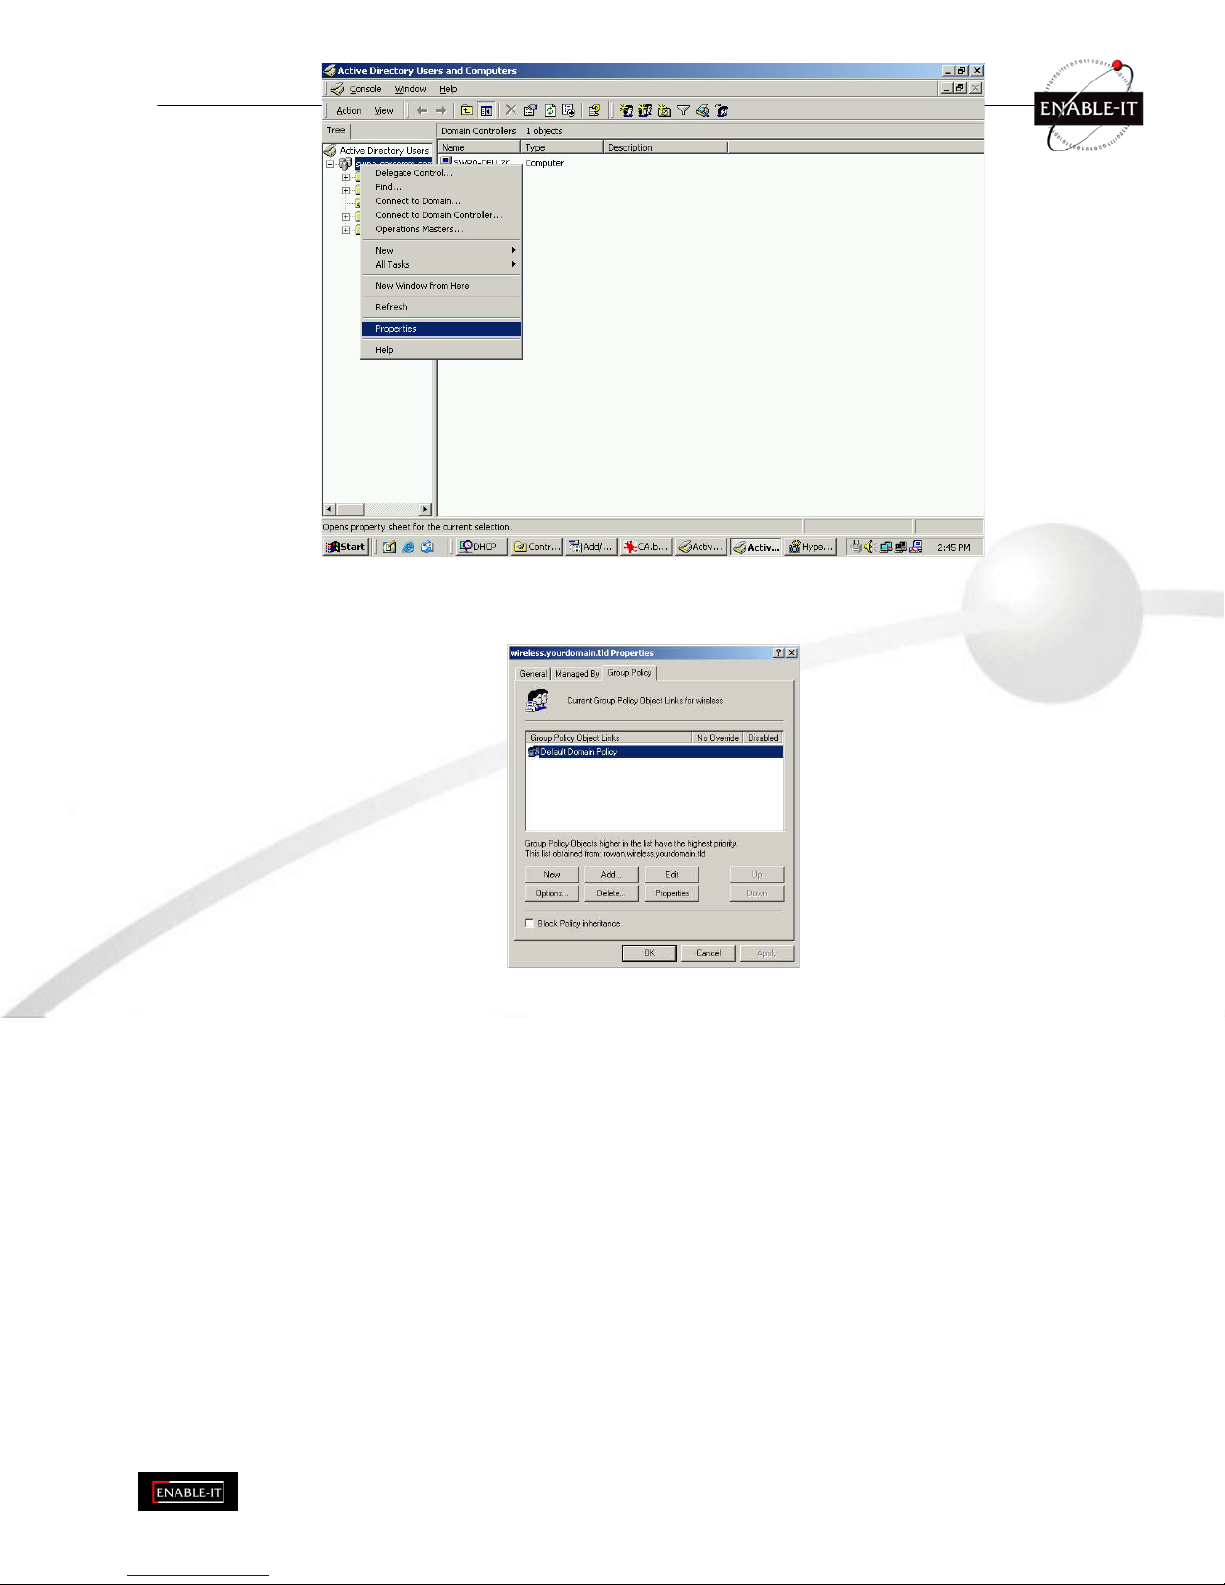
P a g e 5 9 o f
9 3
Figure 52: Active Directory Screen
142. Select the Group Policy tab, choose Default Domain Policy then click Edit.
Figure 53: Group Policy Tab
143. Select Computer Configuration - Windows Settings - Security Settings - Public Key Policies, right-click
Automatic Certificate Request Settings - New - Automatic Certificate Request.
Page 60
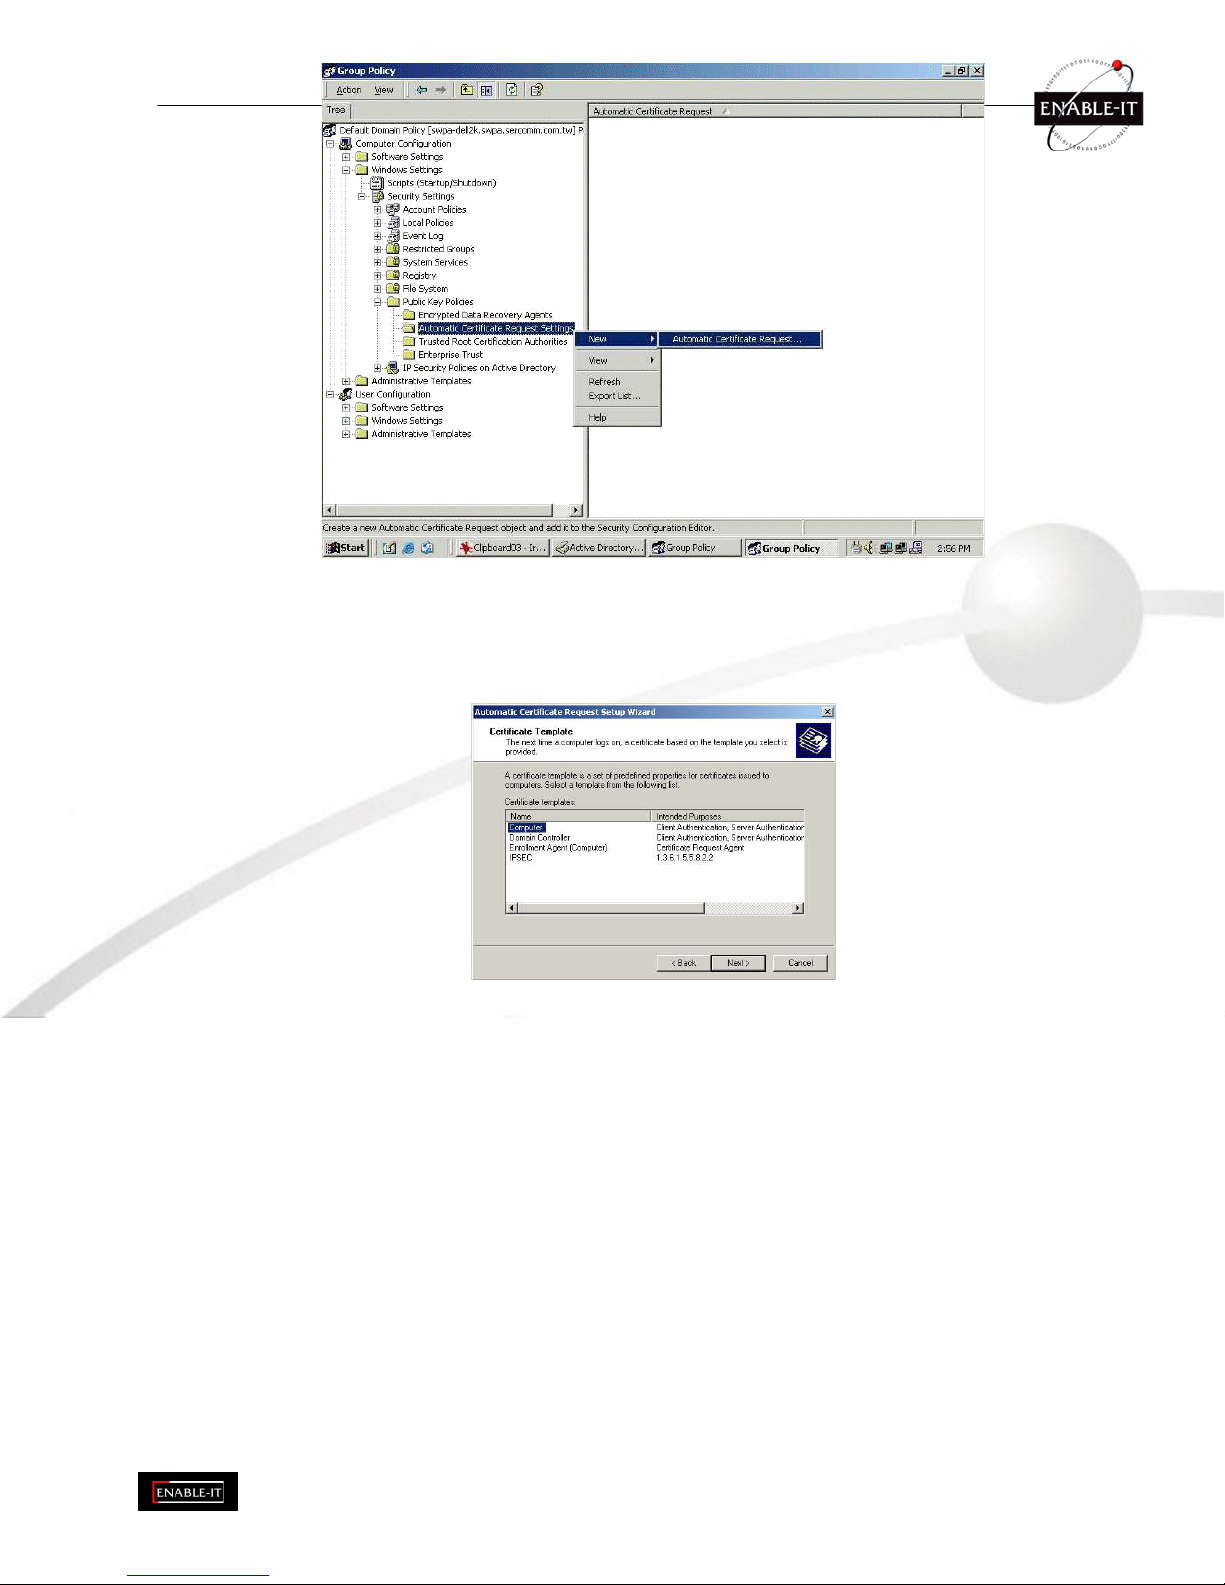
P a g e 6 0 o f
9 3
Figure 54: Group Policy Screen
144. When the Certificate Request Wizard appears, click Next.
145. Select Computer, then click Next.
146.
Figure 55: Certificate Template Screen
147. Ensure that your certificate authority is checked, then click Next.
148. Review the policy change information and click Finish.
149. Click Start - Run, type cmd and press enter.
Enter secedit /refreshpolicy machine_policy
This command may take a few minutes to take effect.
Page 61
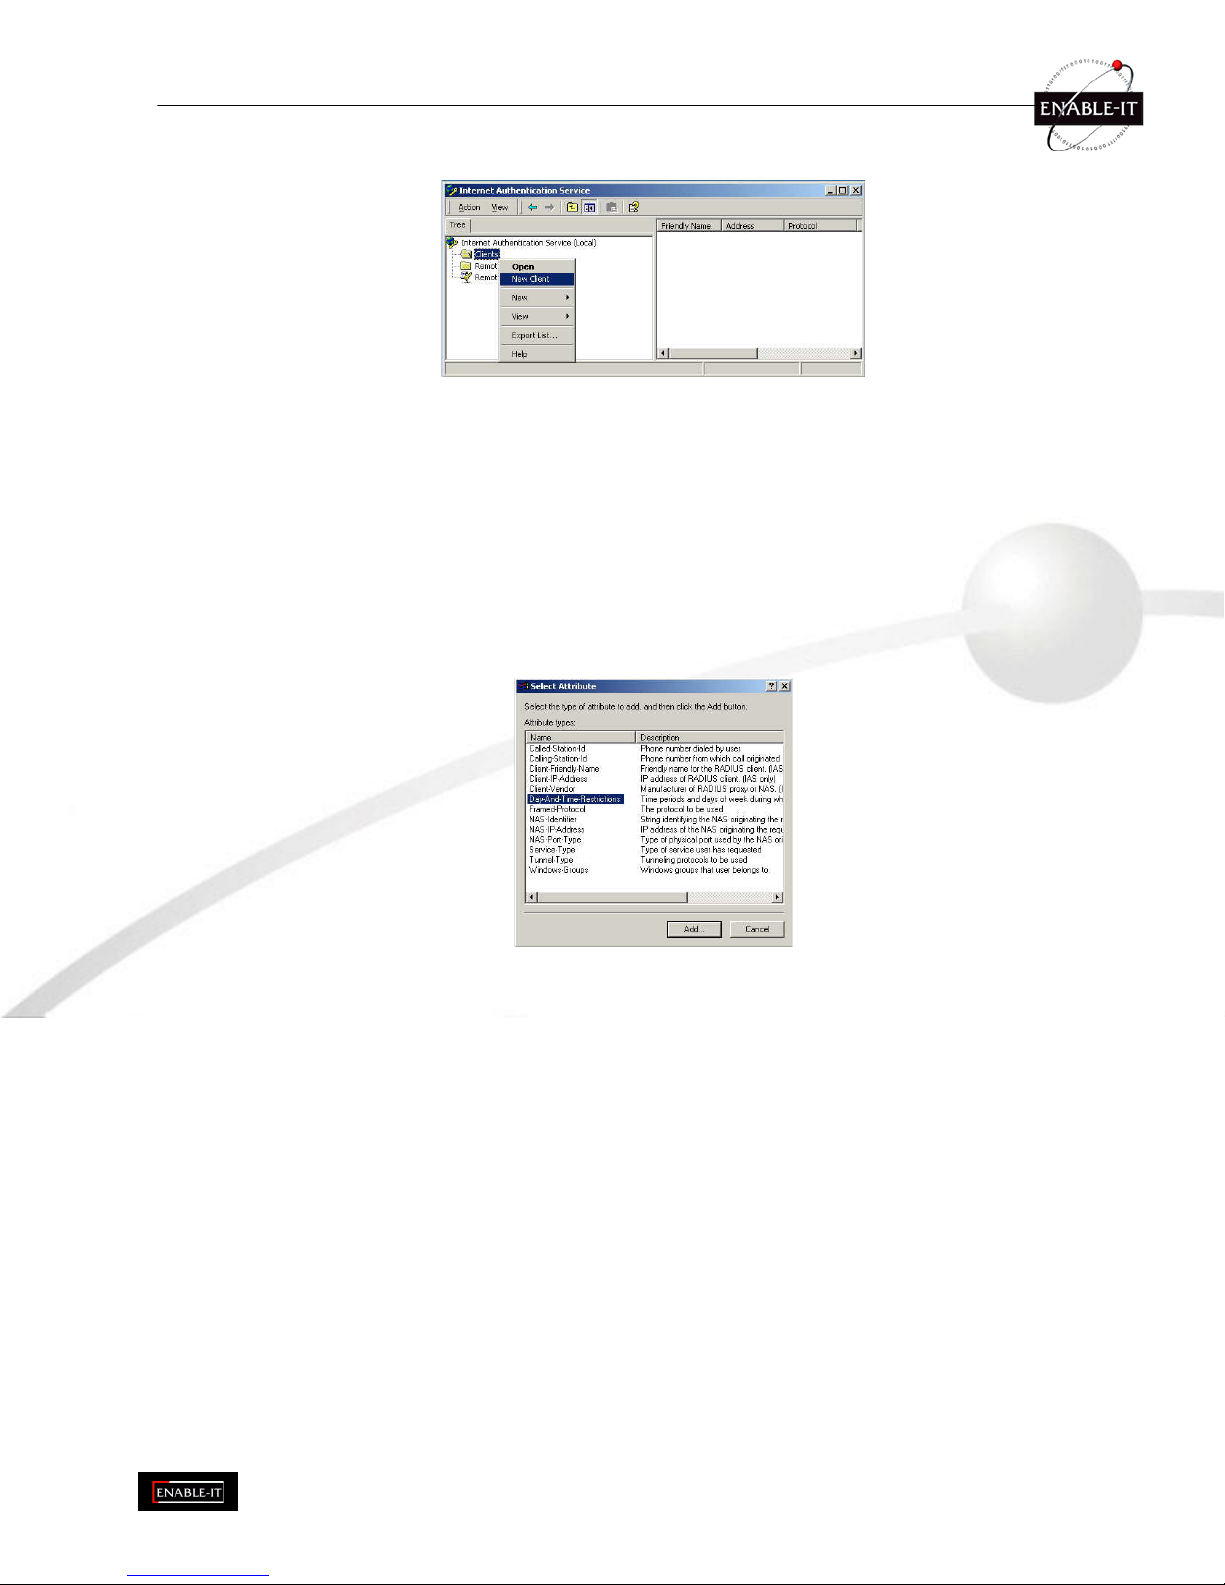
P a g e 6 1 o f
9 3
I n t e r n e t A u t h e n t i c a t i o n S e r v i c e ( R a d i u s ) S e t u p
150. Select Start - Programs - Administrative Tools - Internet Authentication Service
151. Right-click on Clients, and select New Client.
Figure 56: Service Screen
152. Enter a name for the access point, click Next.
153. Enter the address or name of the Wireless Access Point, and set the shared secret, as entered on the
Security Settings of the Wireless Access Point.
154. Click Finish.
155. Right-click on Remote Access Policies, select New Remote Access Policy.
156. Assuming you are using EAP-TLS, name the policy eap-tls, and click Next.
157. Click Add...
If you don't want to set any restrictions and a condition is required, select Day-And-Time-Restrictions, and
click Add...
Figure 57: Attribute Screen
158. Click Permitted, then OK. Select Next.
159. Select Grant remote access permission. Click Next.
160. Click Edit Profile... and select the Authentication tab. Enable Extensible Authentication Protocol, and
select Smart Card or other Certificate. Deselect other authentication methods listed. Click OK.
Page 62
P a g e 6 2 o f
9 3
Figure 58: Authentication Screen
161. Select No if you don't want to view the help for EAP. Click Finish.
Page 63
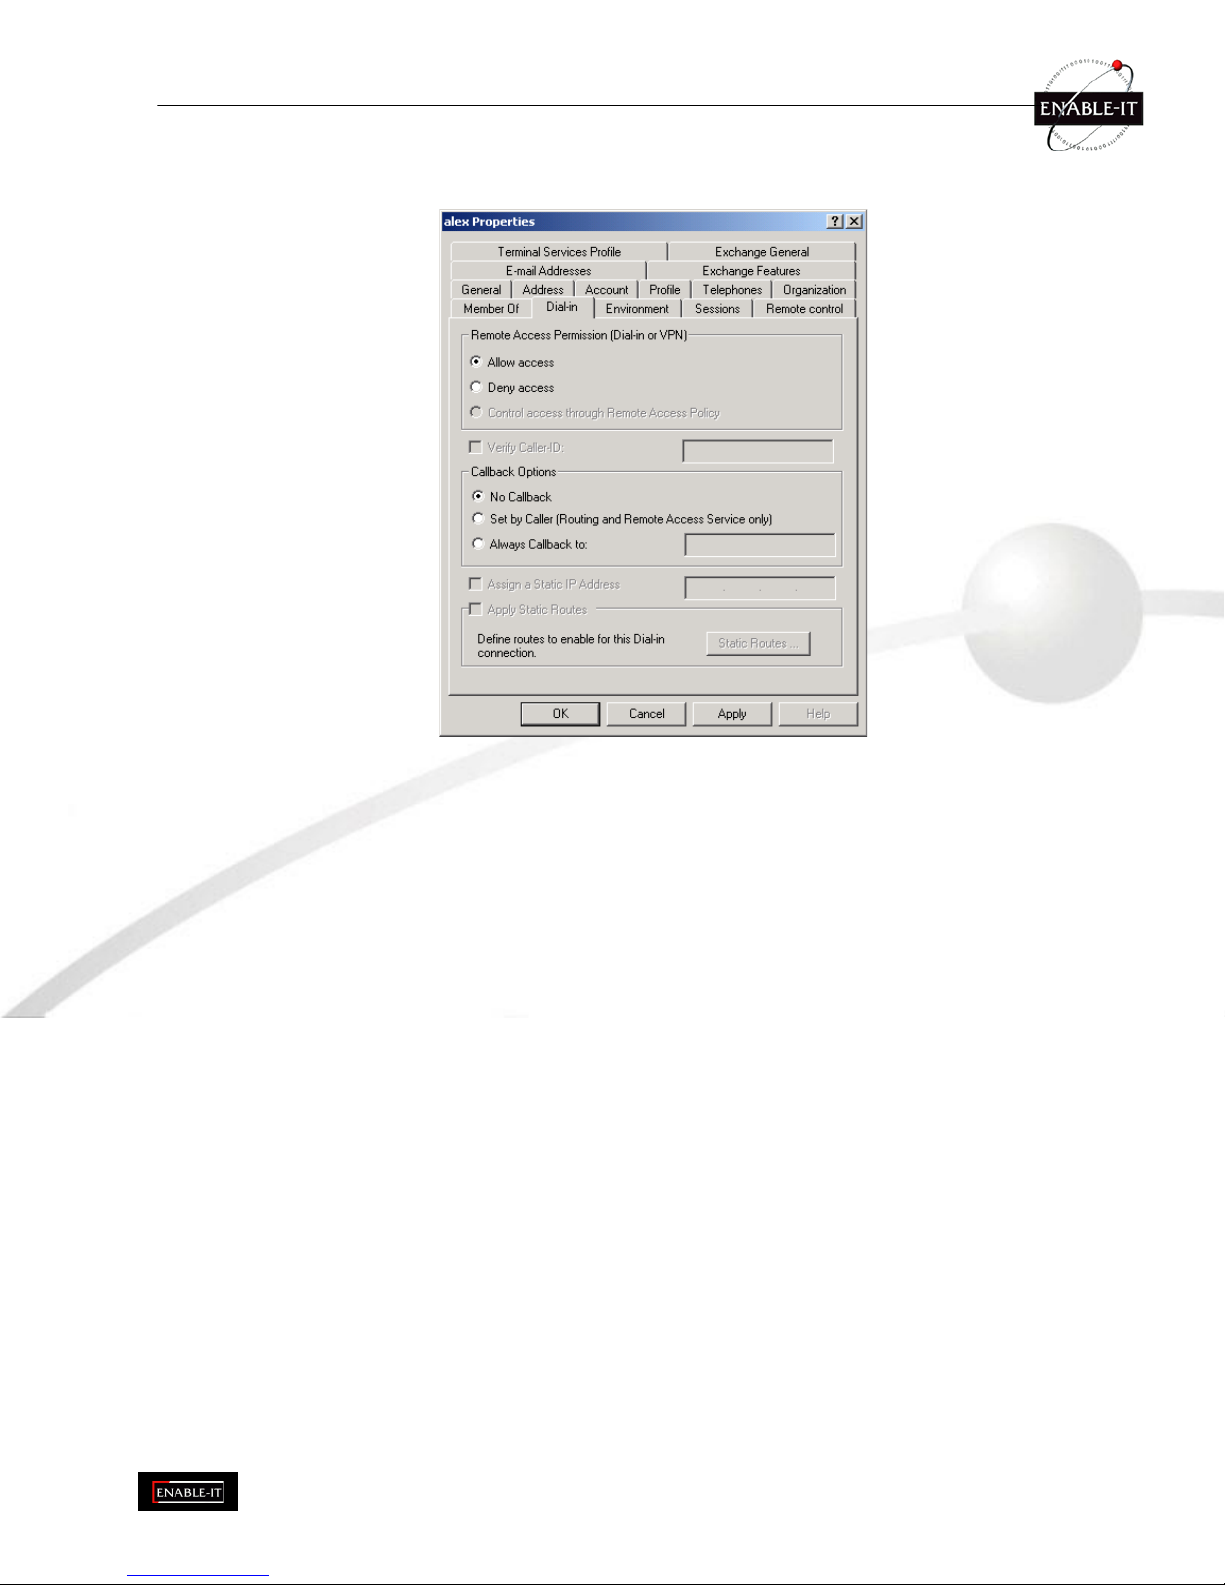
P a g e 6 3 o f
9 3
R e m o t e A c c e s s L o g i n f o r U s e r s
162. Select Start - Programs - Administrative Tools- Active Directory Users and Computers.
163. Double click on the user who you want to enable.
164. Select the Dial-in tab, and enable Allow access. Click OK.
Figure 59: Dial-in Screen
Page 64
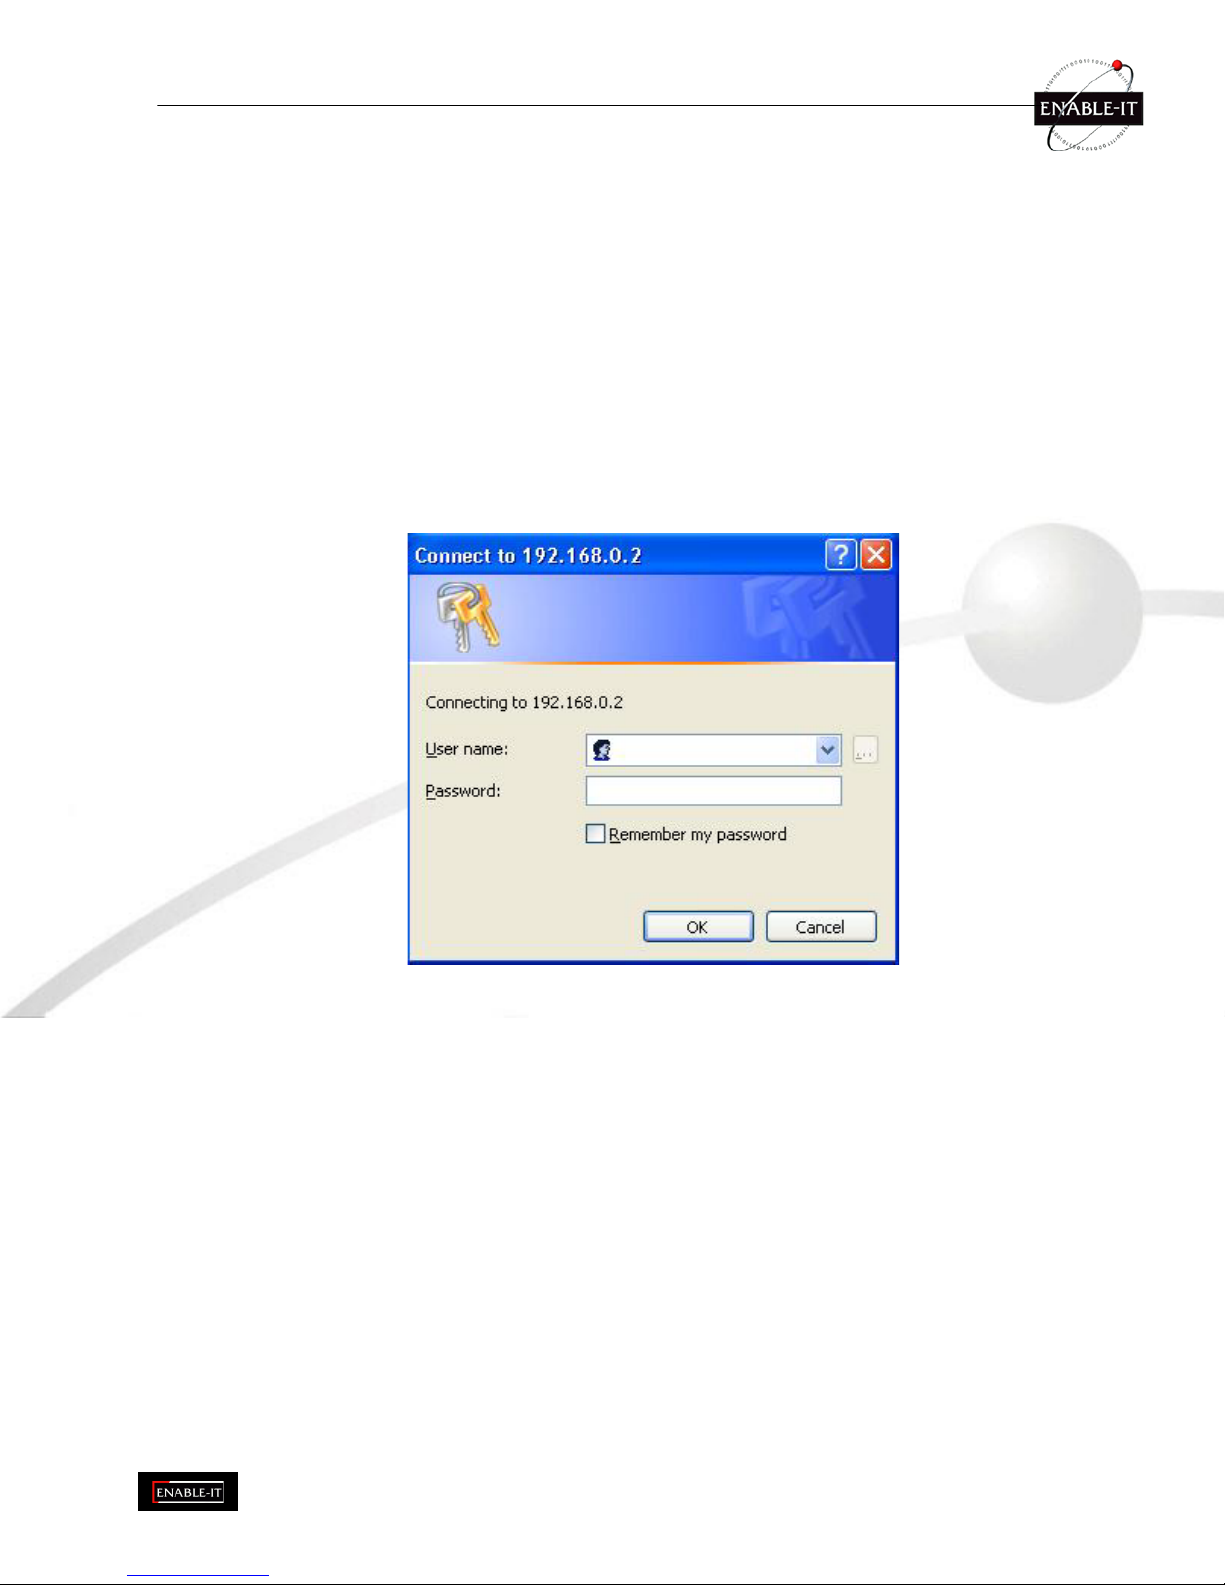
P a g e 6 4 o f
9 3
8 0 2 . 1 x C l i e n t S e t u p o n W i n d o w s X P
W i n d o w s X P s h i p s w i t h a c o m p l e t e 8 0 2 . 1 x c l i e n t i m p l e m e n t a t i o n . I f u s i n g W i n d o w s 2 0 0 0 , y o u c a n i n s t a l l S P 3 ( S e r v i c e
P a c k 3 ) t o g a i n t h e s a m e f u n c t i o n a l i t y .
I f y o u d o n ' t h a v e e i t h e r o f t h e s e s y s t e m s , y o u m u s t u s e t h e 8 0 2 . 1 x c l i e n t s o f t w a r e p r o v i d e d w i t h y o u r w i r e l e s s a d a p t e r .
R e f e r t o y o u r v e n d o r ' s d o c u m e n t a t i o n f o r s e t u p i n s t r u c t i o n s .
T h e f o l l o w i n g i n s t r u c t i o n s a s s u m e t h a t :
• You are using Windows XP
• You are connecting to a Windows 2000 server for authentication.
• You already have a login (User name and password) on the Windows 2000 server.
C l i e n t C e r t i f i c a t e S e t u p
165. Connect to a network which doesn't require port authentication.
166. Start your Web Browser. In the Address box, enter the IP address of the Windows 2000 Server, followed
by /certsrv
e.g
http://192.168.0.2/certsrv
167. You will be prompted for a user name and password. Enter the User name and Password assigned to
you by your network administrator, and click OK.
Figure 60: Connect Screen
168. On the first screen (below), select Request a certificate, click Next.
Page 65
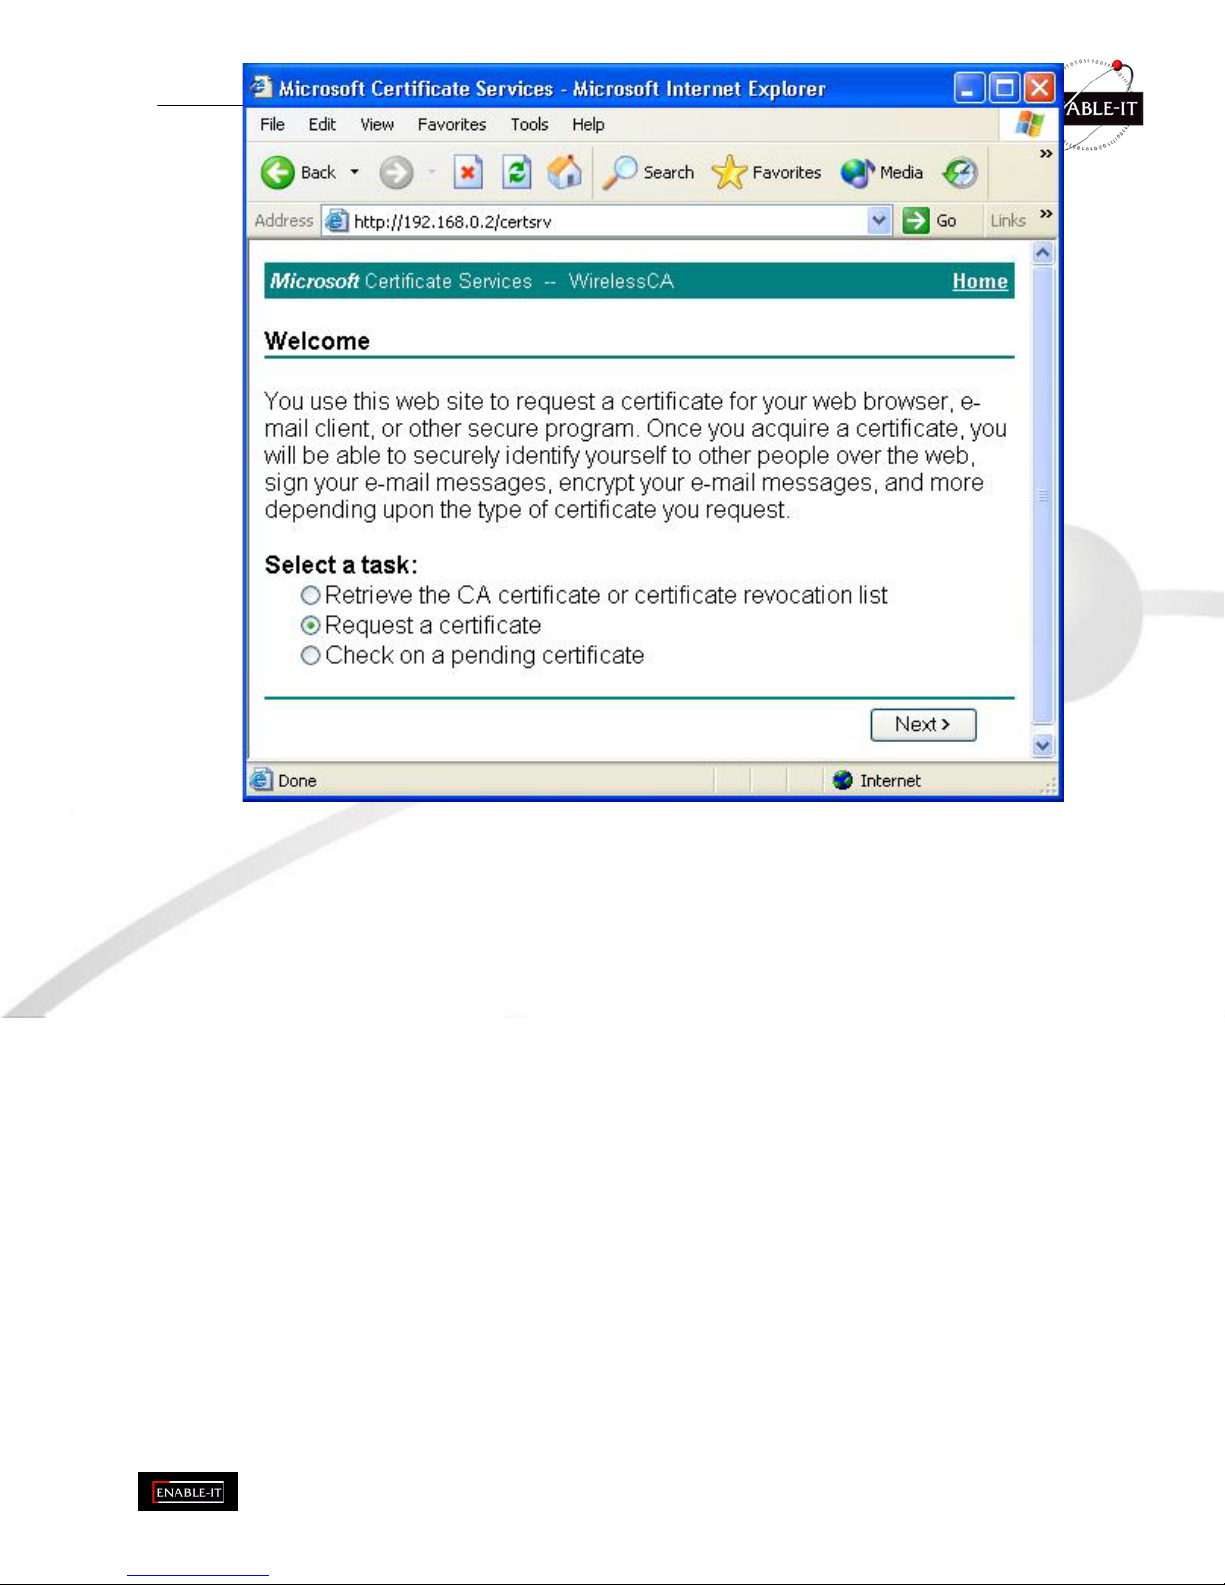
P a g e 6 5 o f
9 3
Figure 61: Wireless CA Screen
169. Select User certificate request and select User Certificate, the click Next.
Page 66
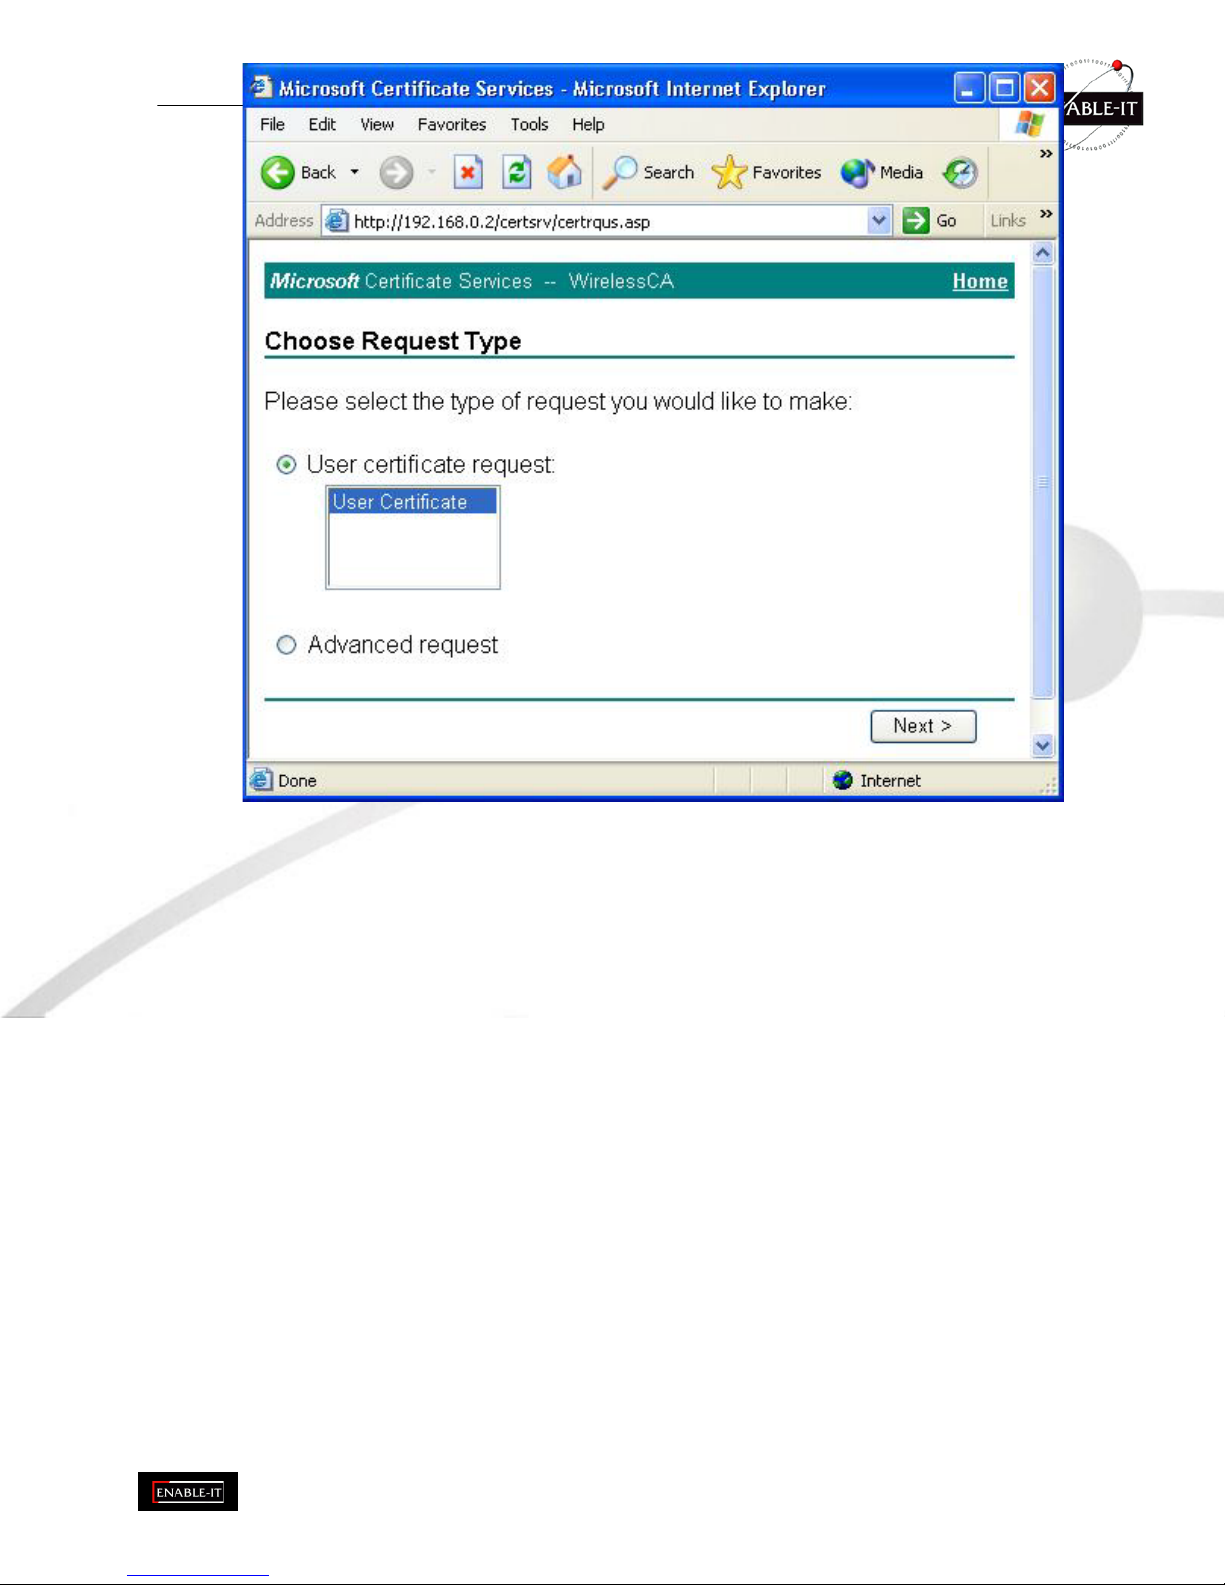
P a g e 6 6 o f
9 3
Figure 62: Request Type Screen
170. Click Submit.
Page 67
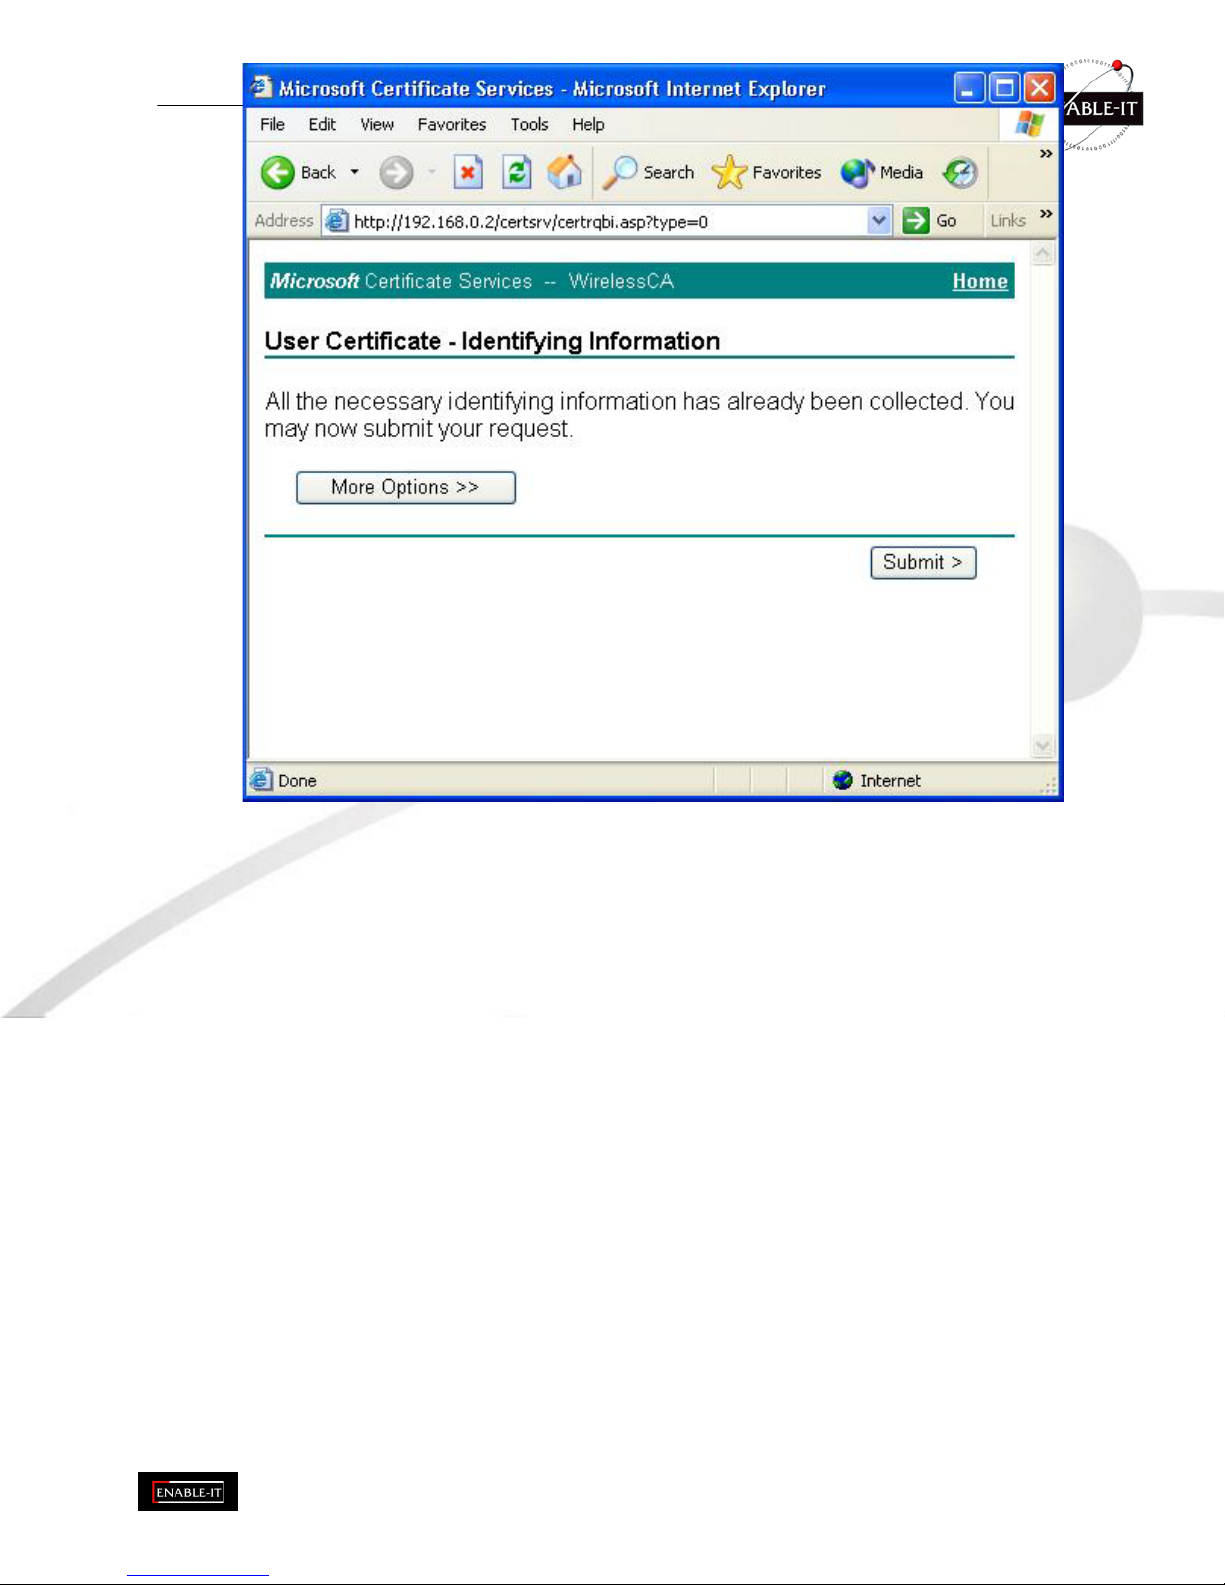
P a g e 6 7 o f
9 3
Figure 63: Identifying Information Screen
171. A message will be displayed, then the certificate will be returned to you.
Click Install this certificate.
Page 68
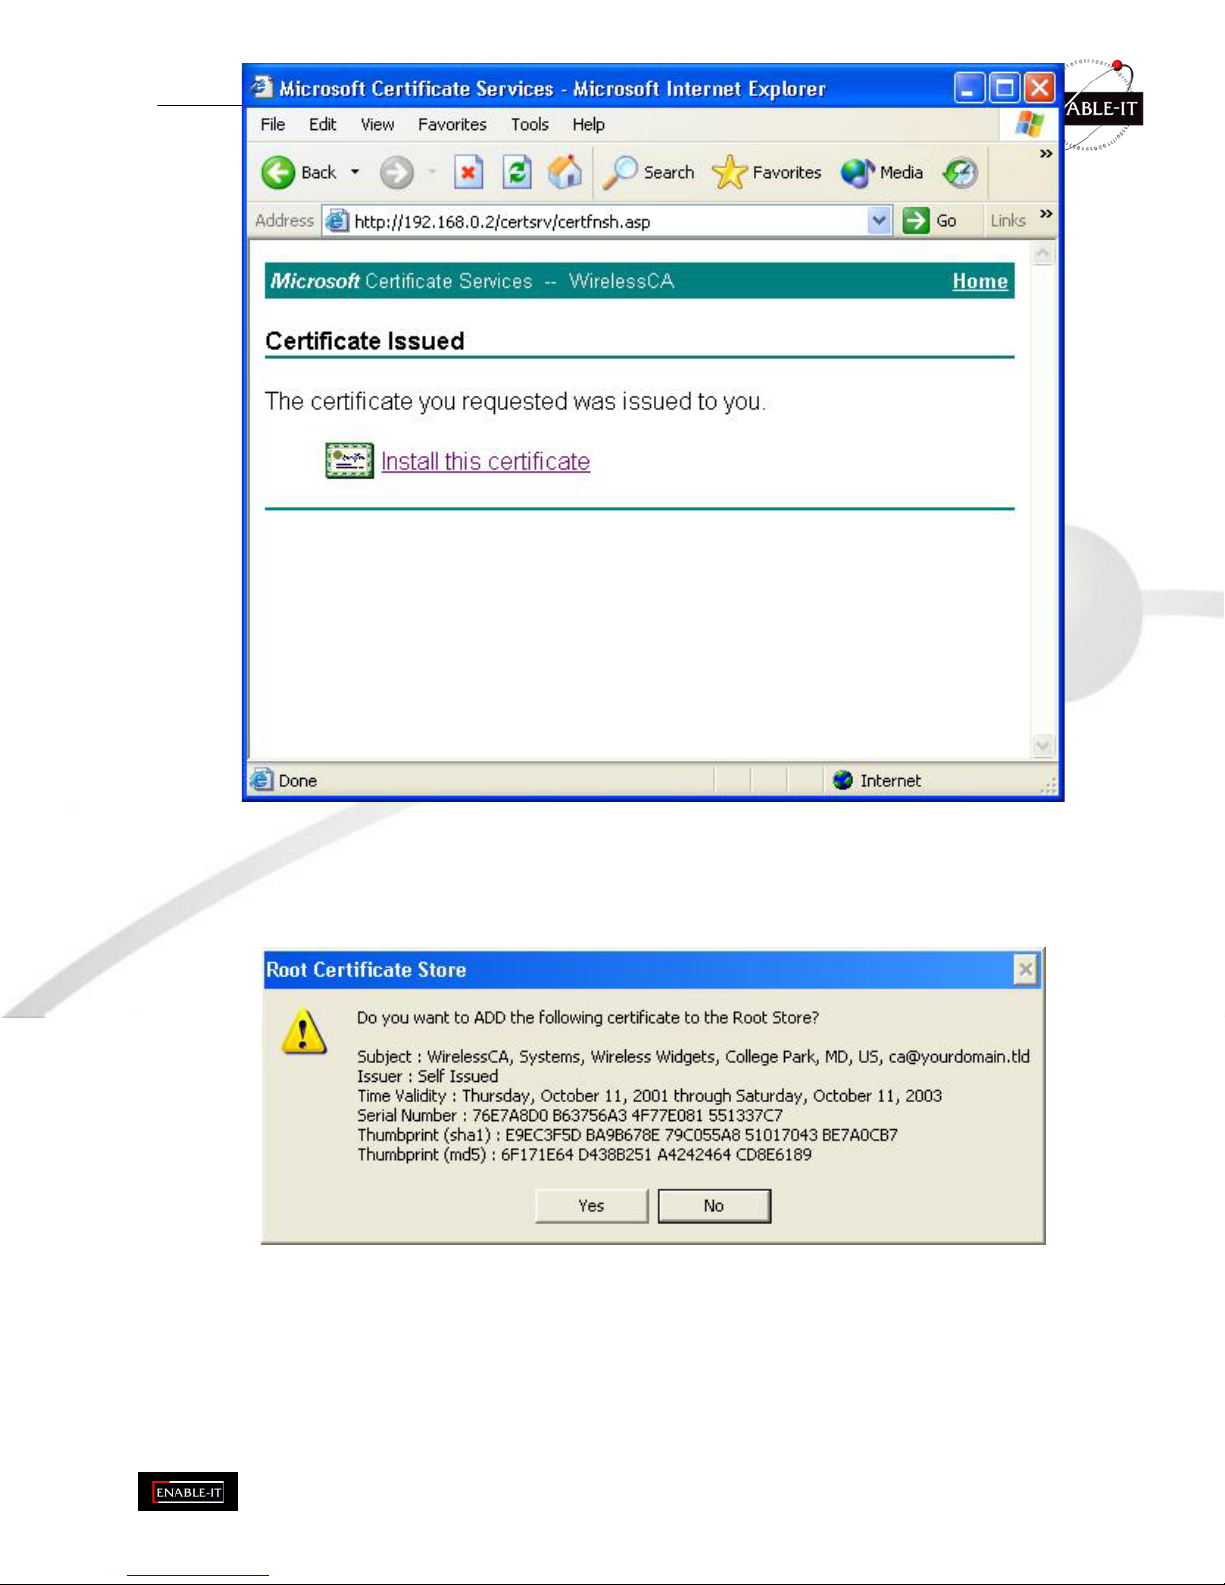
P a g e 6 8 o f
9 3
Figure 64:Certificate Issued Screen
172. . You will receive a confirmation message. Click Yes.
173.
Figure 65: Root Certificate Screen
174. Certificate setup is now complete.
8 0 2 . 1 x A u t h e n t i c a t i o n S e t u p
175. Open the properties for the wireless connection, by selecting Start - Control Panel - Network
Connections.
176. Right Click on the Wireless Network Connection, and select Properties.
Page 69
P a g e 6 9 o f
9 3
177. Select the Authentication Tab, and ensure that Enable network access control using IEEE 802.1X is
selected, and Smart Card or other Certificate is selected from the EAP type.
Figure 66: Authentication Tab
E n c r y p t i o n S e t t i n g s
T h e E n c r y p t i o n s e t t i n g s m u s t m a t c h t h e A P s ( A c c e s s P o i n t s ) o n t h e W i r e l e s s n e t w o r k y o u w i s h t o j o i n .
• Windows XP will detect any available Wireless networks, and allow you to configure each network
independently.
• Your network administrator can advise you of the correct settings for each network. 802.1x networks typically
use EAP-TLS. This is a dynamic key system, so there is no need to enter key values.
E n a b l i n g E n c r y p t i o n
To e n a b l e e n c r y p t i o n f o r a w i r e l e s s n e t w o r k , f o l l o w t h i s p r o c e d u r e :
178. Click on the Wireless Networks tab.
Page 70
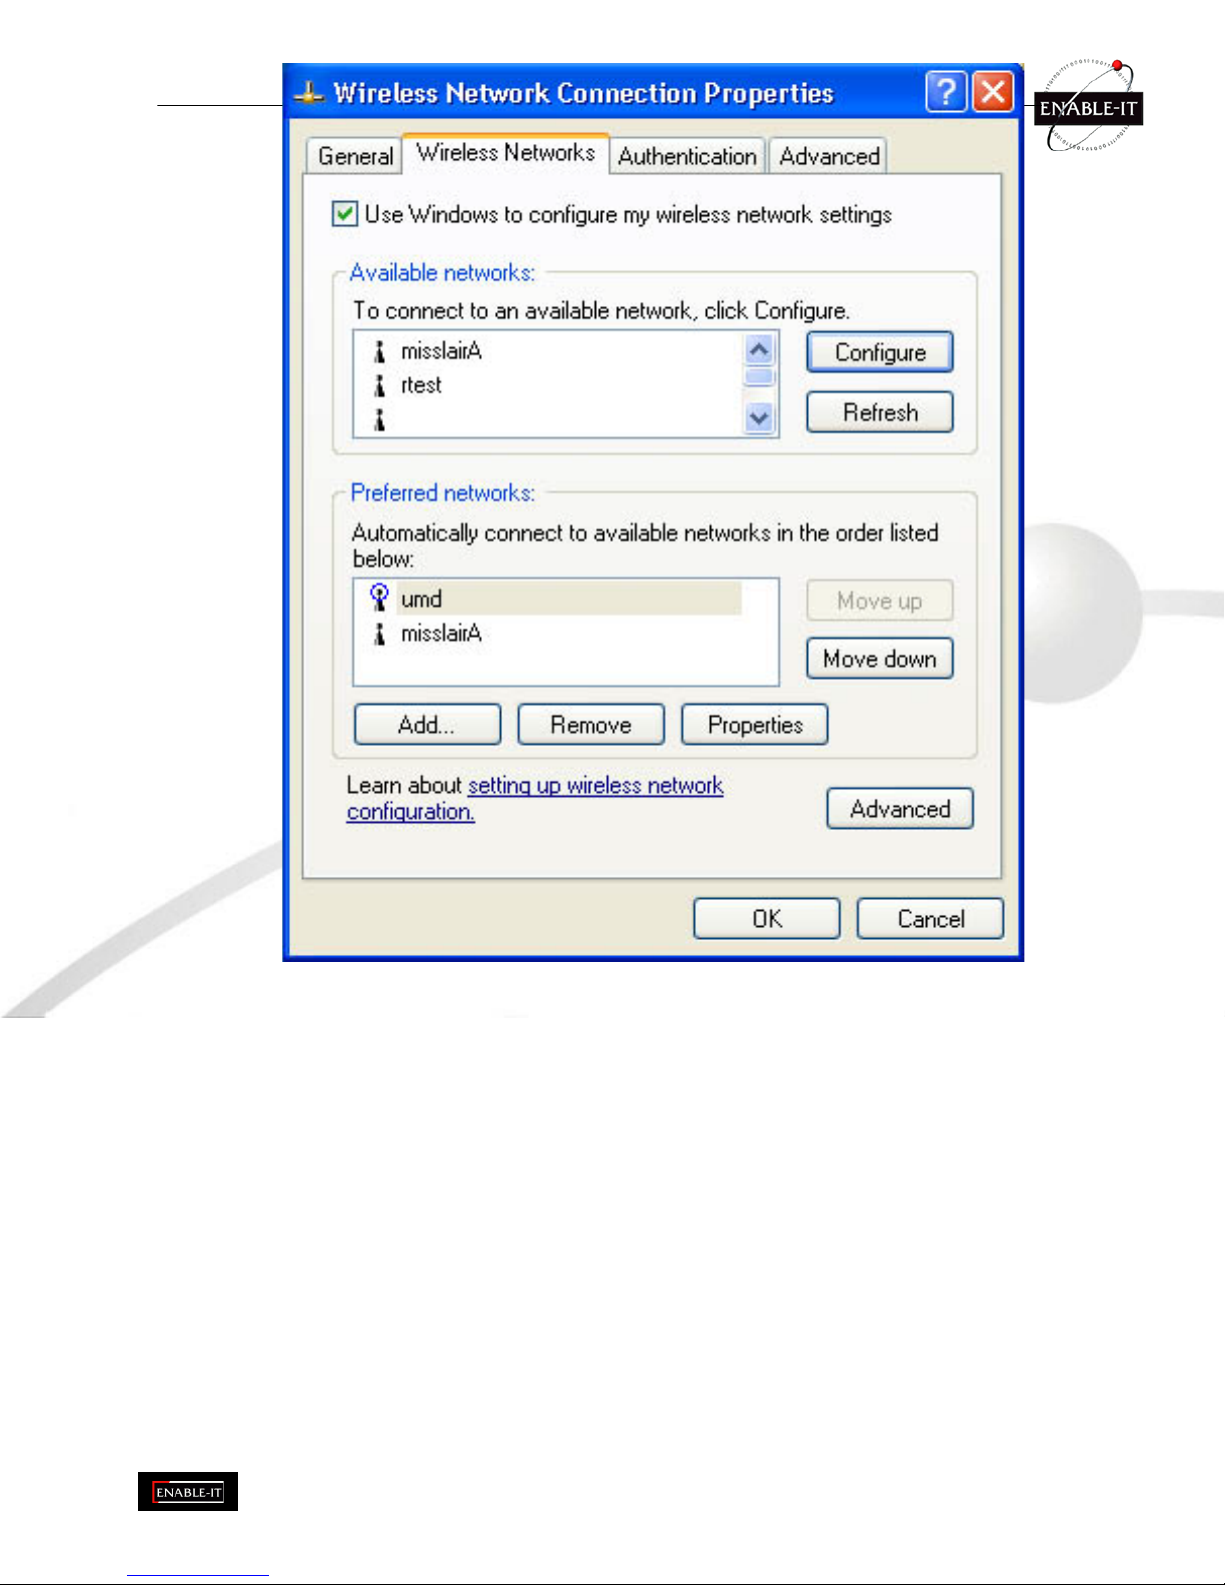
P a g e 7 0 o f
9 3
Figure 67: Wireless Networks Screen
179. Select the wireless network from the Available Networks list, and click Configure.
180. Select and enter the correct values, as advised by your Network Administrator.
For example, to use EAP-TLS, you would enable Data encryption, and click the checkbox for the setting The
key is provided for me automatically, as shown below.
Page 71
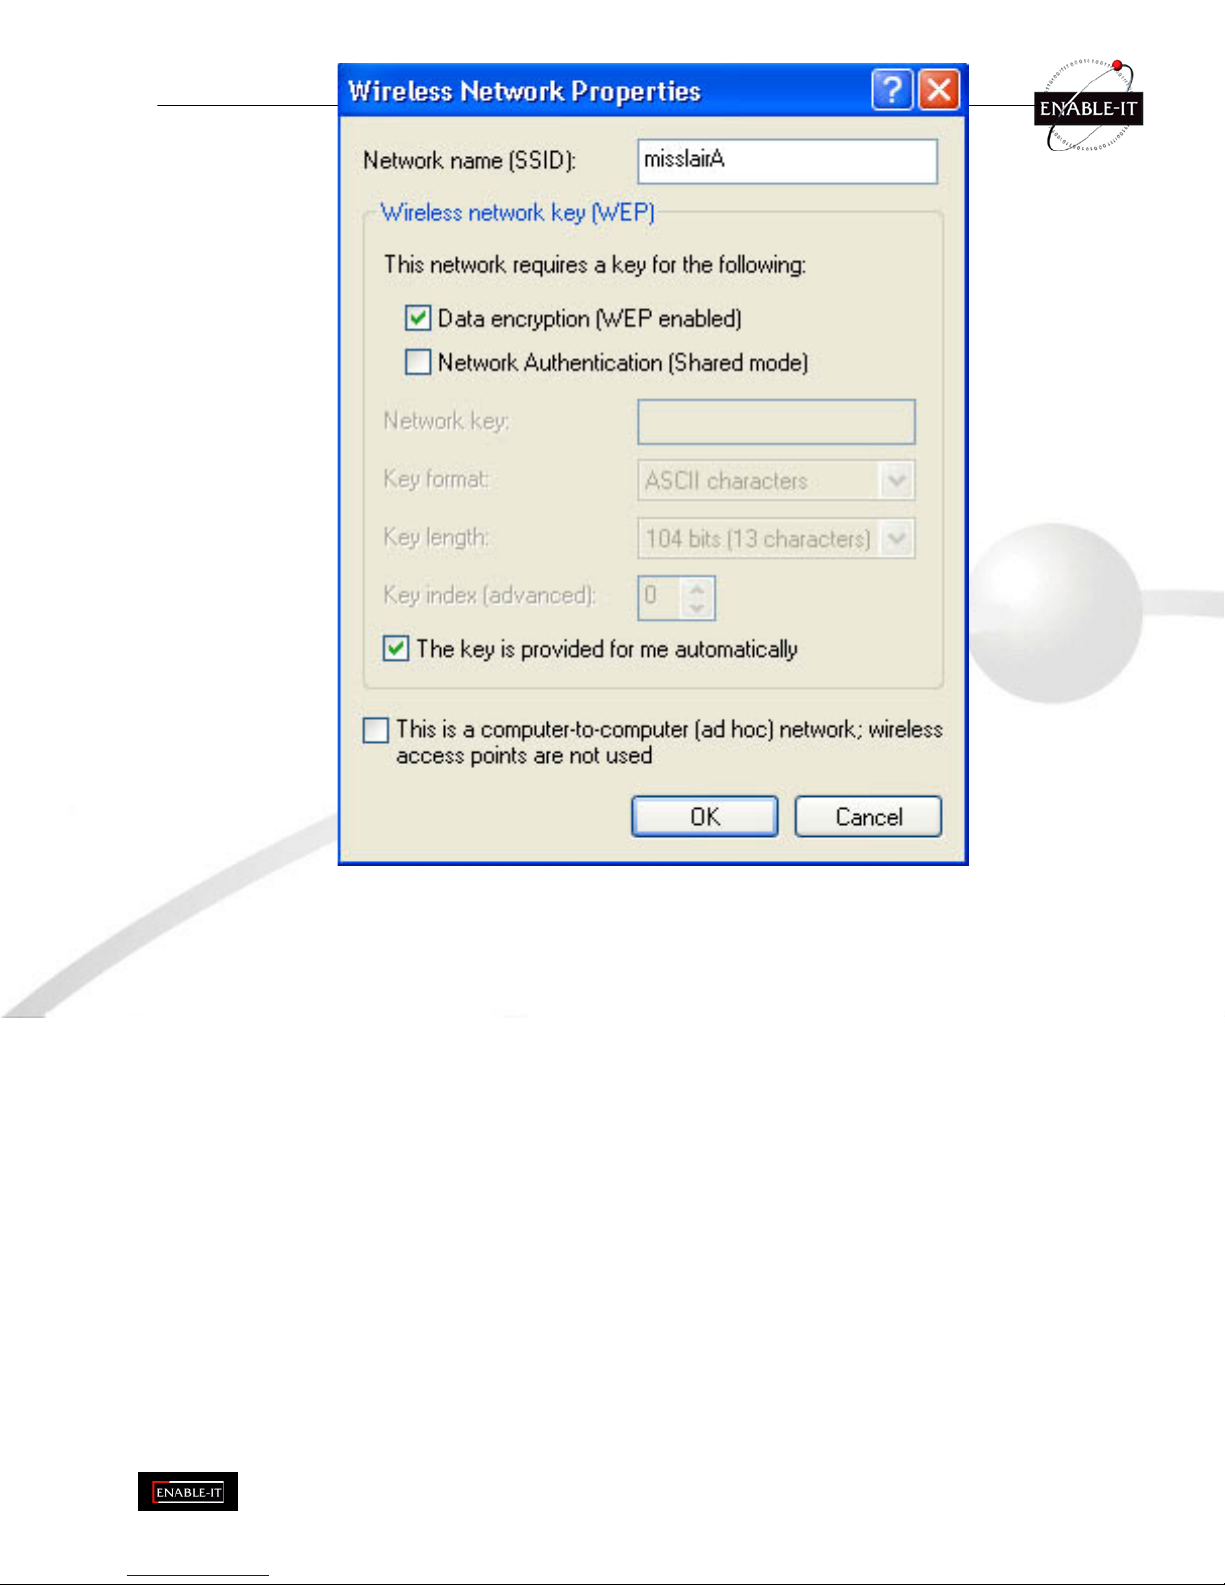
P a g e 7 1 o f
9 3
Figure 68: Properties Screen
S e t u p f o r W i n d o w s X P a n d 8 0 2 . 1 x c l i e n t i s n o w c o m p l e t e .
Page 72
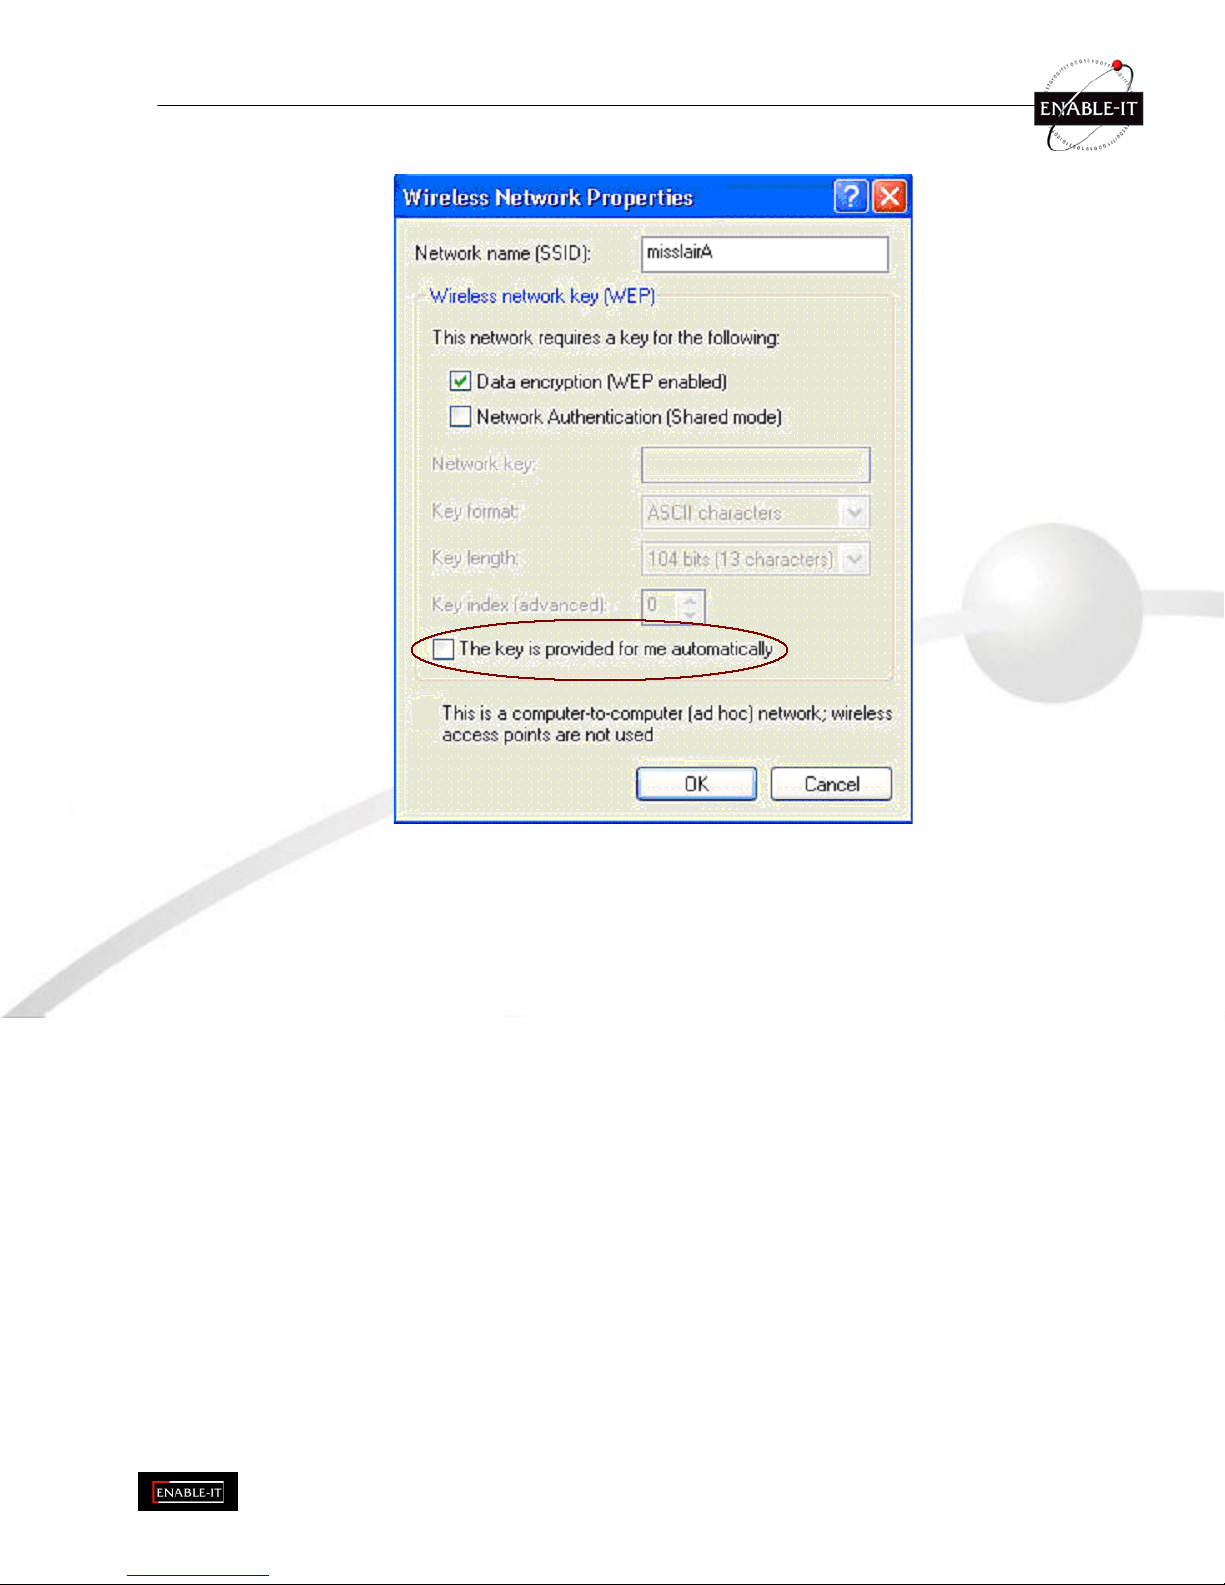
P a g e 7 2 o f
9 3
U s i n g 8 0 2 . 1 x M o d e ( w i t h o u t W P A )
T h i s i s v e r y s i m i l a r t o u s i n g W P A -8 0 2 . 1 x .
T h e o n l y d i f f e r e n c e i s t h a t o n y o u r c l i e n t , y o u m u s t N O T e n a b l e t h e s e t t i n g T h e k e y i s p r ov i d e d f o r m e a u t o m a t i c a l l y .
I n s t e a d , y o u m u s t e n t e r t h e W E P k e y m a n u a l l y , e n s u r i n g i t m a t c h e s t h e W E P k e y u s e d o n t h e A c c e s s P o i n t .
Figure 69: Properties Screen
N o t e :
O n s o m e s y s t e m s , t h e " 6 4 b i t " W E P k e y i s s h o w n a s " 4 0 b i t " a n d t h e " 1 2 8 b i t " W E P k e y i s s h o w n a s " 1 0 4 b i t " . T h i s
d i f f e r e n c e a r i s e s b e c a u s e t h e k e y i n p u t b y t h e u s e r i s 2 4 b i t s l e s s t h a n t h e k e y s i z e u s e d f o r e n c r y p t i o n .
C h a p t e r 5
O p e r a t i o n a n d S t a t u s
This Chapter details the operation of the Wireless Access Point and the status screens.
O p e r a t i o n
O n c e b o t h t h e W i r e l e s s A c c e s s P o i n t a n d t h e P C s a r e c o n f i g u r e d , o p e r a t i o n i s a u t om a t i c .
H o w e v e r , y o u m a y n e e d t o p e r f o r m t h e f o l l o w i n g o p e r a t i o n s o n a r e g u l a r b a s i s .
• If using the Access Control feature, update the Trusted PC database as required. (See Access Control in
Chapter 3 for details.)
• If using 802.1x mode, update the User Login data on the Windows 2000 Server, and configure the client PCs,
as required.
S t a t u s S c r e e n
U s e t h e S t a t u s l i n k o n t h e m a i n m e n u t o v i e w t h i s s c r e e n .
Page 73
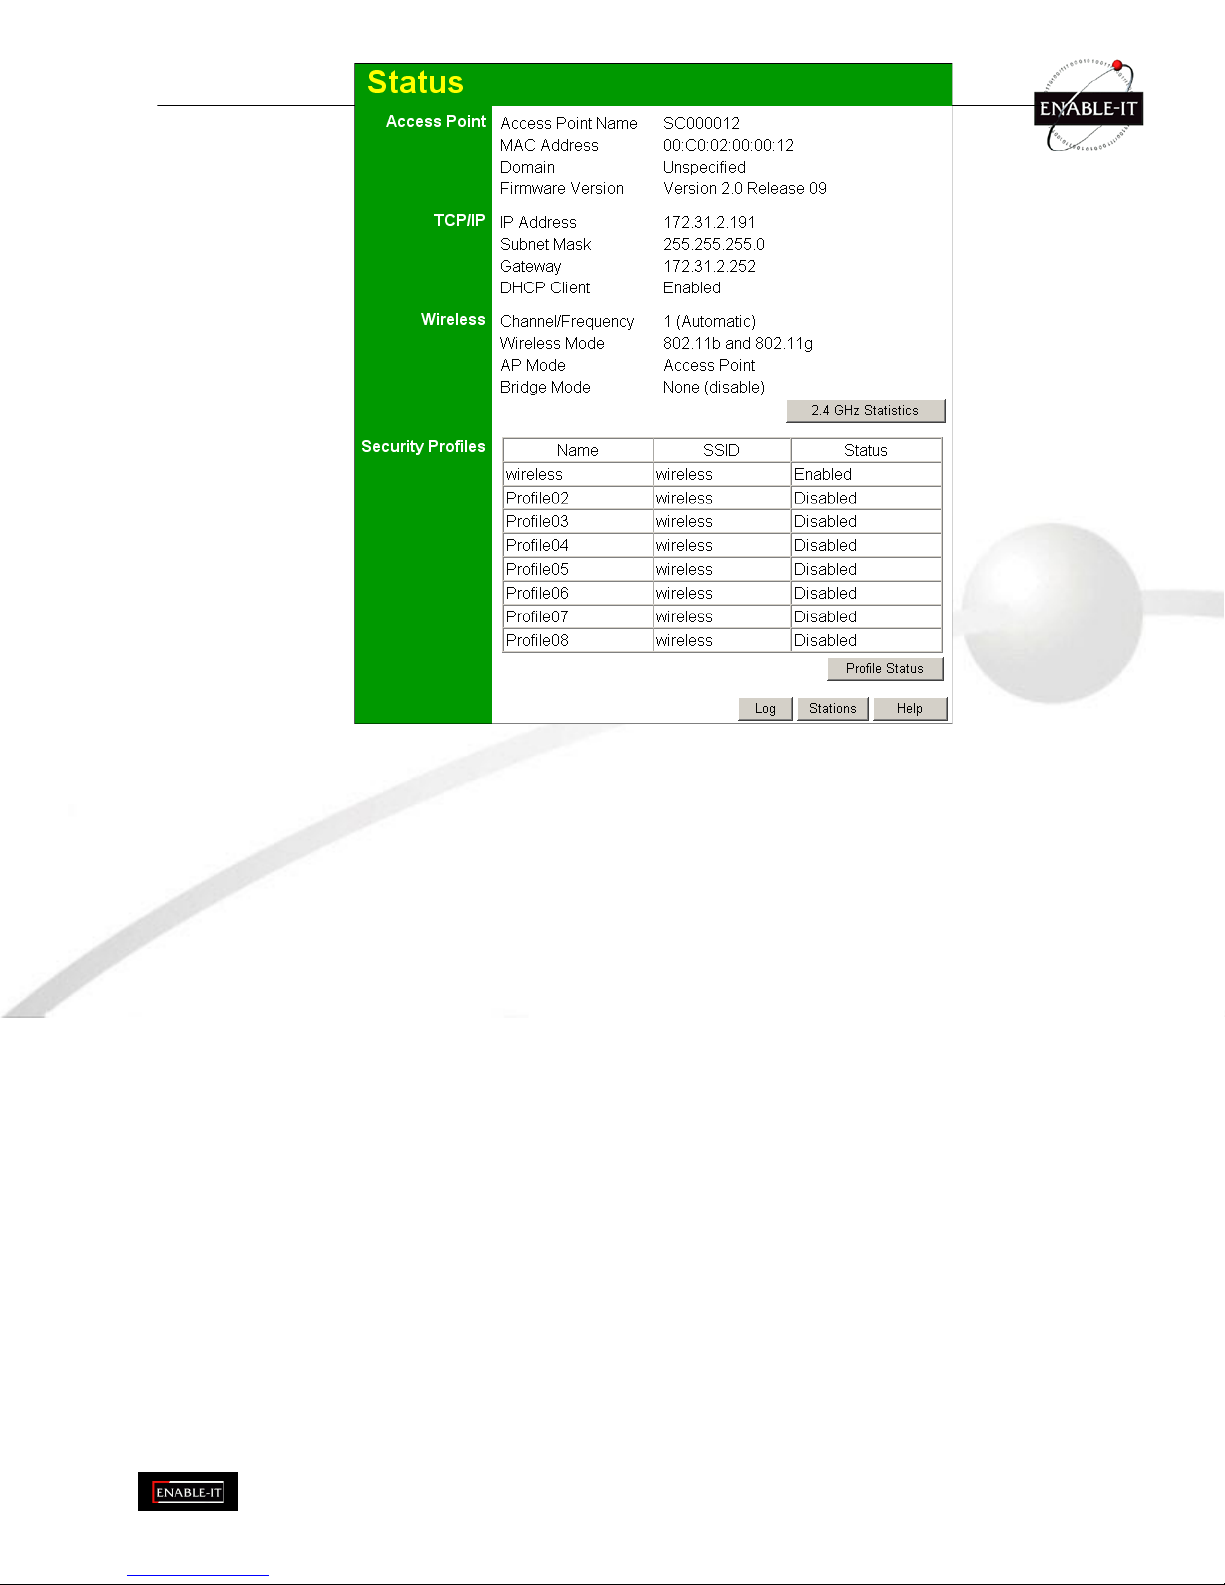
P a g e 7 3 o f
9 3
Figure 70: Status Screen
Page 74
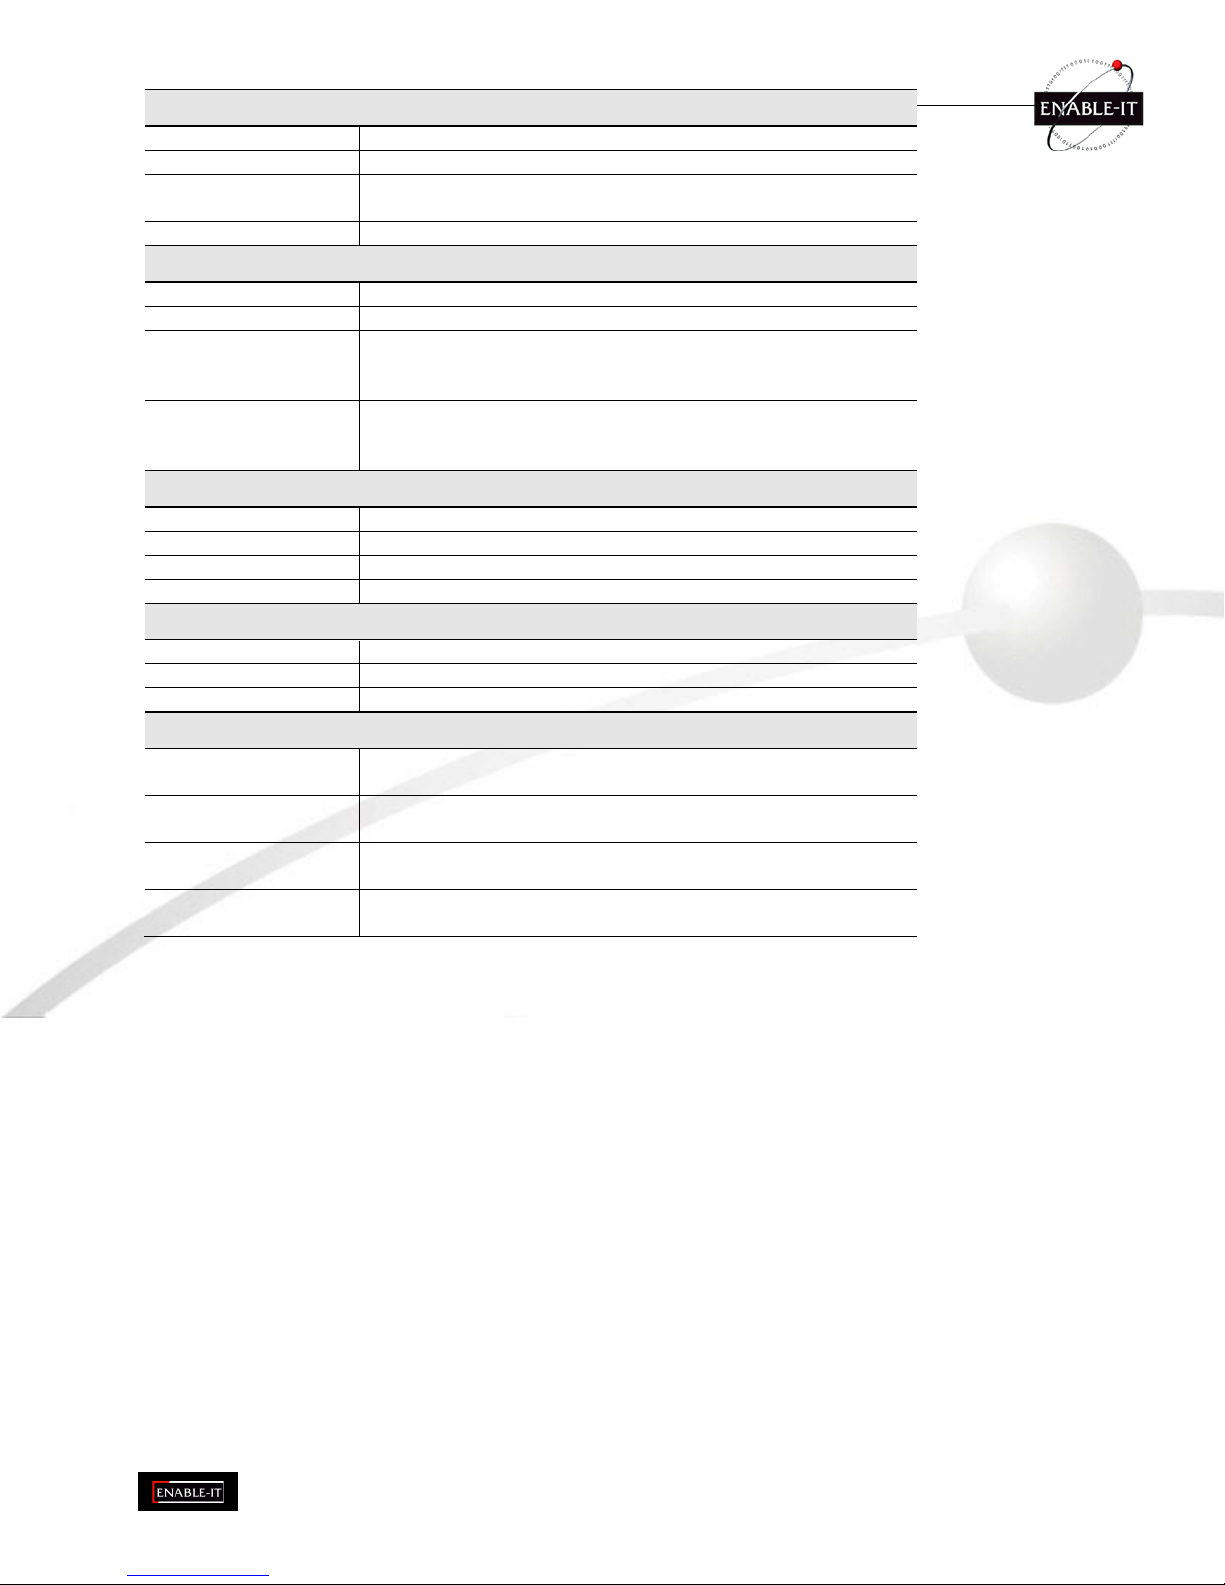
P a g e 7 4 o f
9 3
D a t a - S t a t u s S c r e e n
Access Point
A c c e s s P o i n t N a m e
T h e c u r r e n t n a m e w i l l b e d i s p l a y e d .
M A C A d d r e s s
T h e M A C ( p h y s i c a l ) a d d r e s s o f t h e W i r e l e s s A c c e s s P o i n t .
D o m a i n
T h e r e g i o n o r d o m a i n , a s s e l e c t e d o n t h e B a s i c W i r e l e s s
s c r e e n .
F i r m w a r e V e r s i o n
T h e v e r s i o n o f t h e f i r m w a r e c u r r e n t l y i n s t a l l e d .
TCP/IP
I P A d d r e s s
T h e I P A d d r e s s o f t h e W i r e l e s s A c c e s s P o i n t .
S u b n e t M a s k
T h e N e t w o r k M a s k ( S u b n e t M a s k ) f o r t h e I P A d d r e s s a b o v e .
G a t e w a y
E n t e r t h e G a t e w a y f o r t h e L A N s e g m e n t t o w h i c h t h e W i r el e s s
A c c e s s P o i n t i s a t t a c h e d ( t h e s a m e v a l u e a s t h e P C s o n t h a t
L A N s e g m e n t ) .
D H C P C l i e n t
T h i s i n d i c a t e s w h e t h e r t h e c u r r e n t I P a d d r e s s w a s o b t a i n e d
f r o m a D H C P S e r v e r o n y o u r n e t w o r k .
I t w i l l d i s p l a y " E n a b l e d " o r " D i sa b l e d " .
Wireless
C h a n n e l / F r e q u e n c y
T h e C h a n n e l c u r r e n t l y i n u s e i s d i s p l a y e d .
W i r e l e s s M o d e
T h e c u r r e n t m o d e ( e . g . 8 0 2 . 1 1 g ) i s d i s p l a y e d .
A P M o d e
T h e c u r r e n t A c c e s s P o i n t m o d e i s d i s p l a y e d .
B r i d g e M o d e
T h e c u r r e n t B r i d g e m o d e i s d i s p l a y e d .
Security Profiles
N a m e
T h i s d i s p l a y s t h e c u r r e n t n a m e o f e a c h s e c u r i t y p r o f i l e .
S S I D
T h i s d i s p l a y s t h e S S I D a s s o c i a t e d w i t h t h e p r o f i l e .
S t a t u s
T h i s i n d i c a t e s w h e t h e r o r n o t t h e p r o f i l e i s e n a b l e d .
Buttons
S t a t i s t i c s
C l i c k t h i s t o o p e n a s u b -w i n d o w w h e r e y o u c a n v i e w S t a t i st i c s
o n d a t a t r a n s m i t t e d o r r e c e i v e d b y t h e A c c e s s P o i n t .
P r o f i l e S t a t u s
C l i c k t h i s t o o p e n a s u b -w i n d o w w h i c h d i s p l a y s f u r t h e r d e t a i l s
a b o u t e a c h s e c u r i t y p r o f i l e .
L o g
C l i c k t h i s t o o p e n a s u b -w i n d o w w h e r e y o u c a n v i e w t h e a c t i v i t y
l o g .
S t a t i o n s
C l i c k t h i s t o o p e n a s u b -w i n d o w w h e r e y o u c a n v i e w t h e l i s t o f
a l l c u r r e n t W i r e l e s s S t at i o n s u s i n g t h e A c c e s s P o i n t .
Page 75
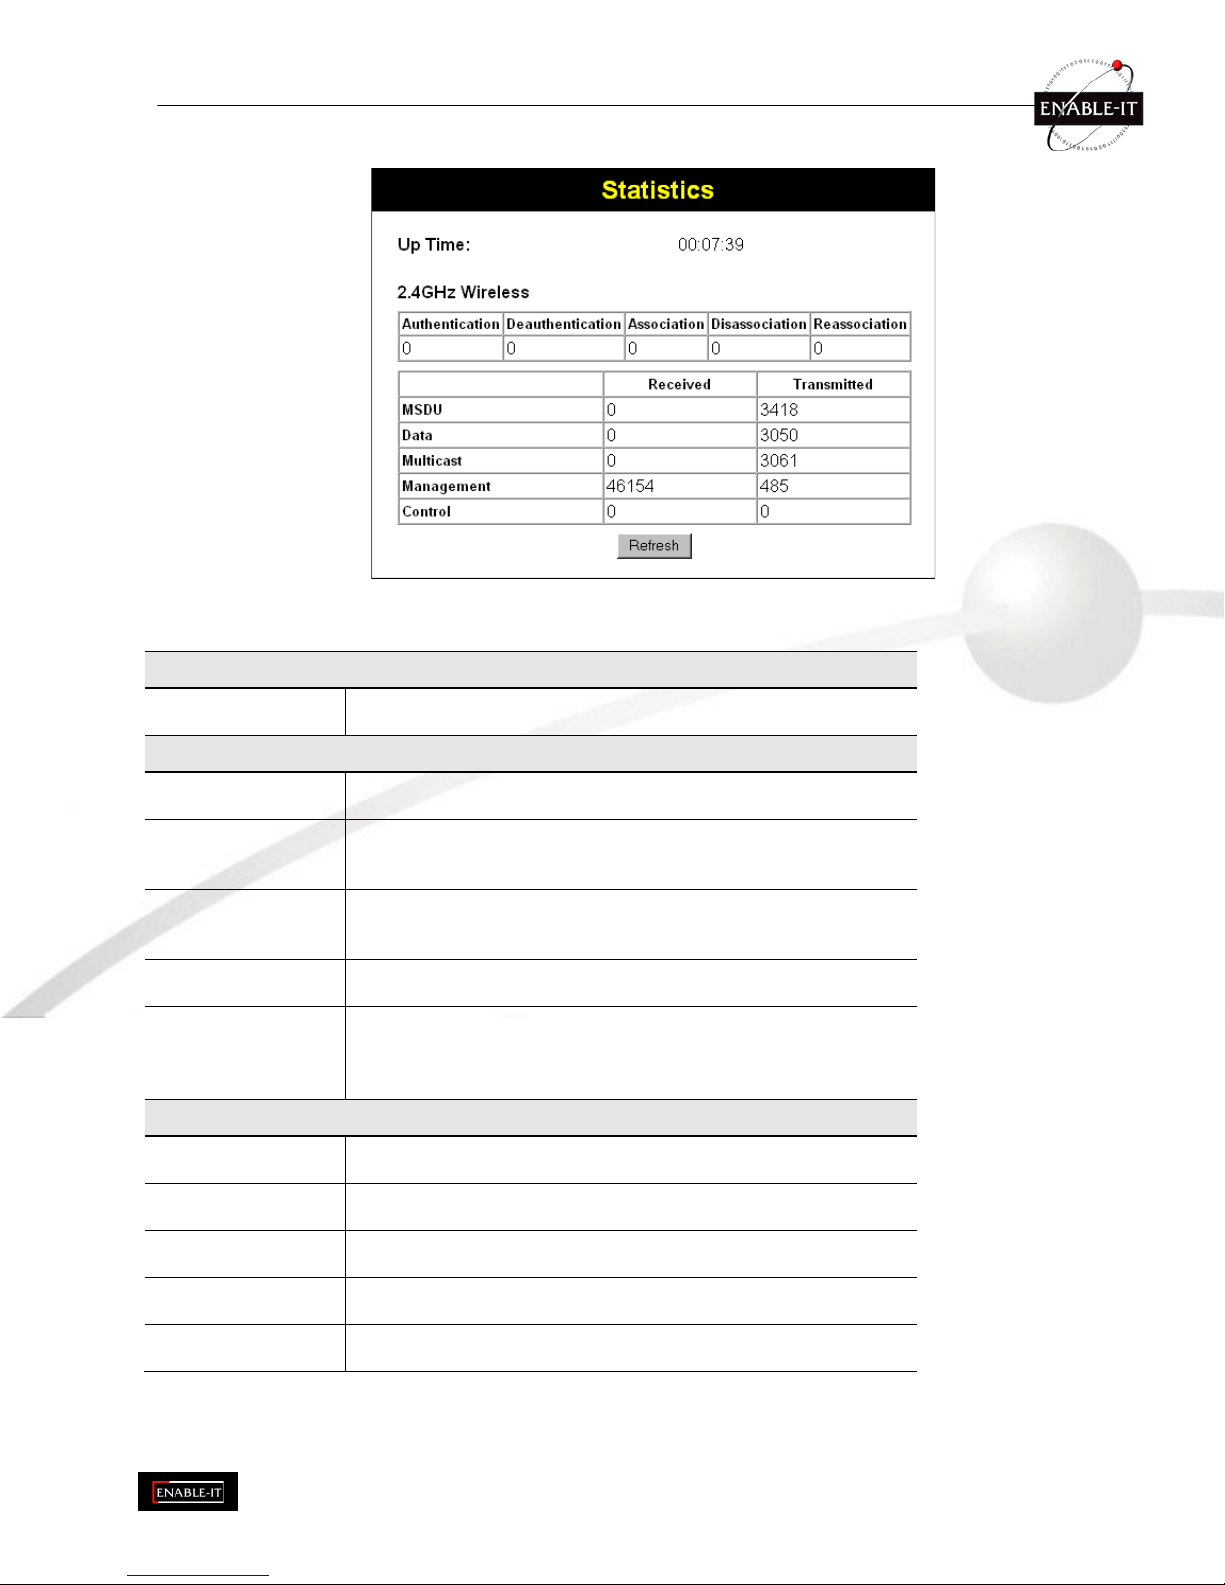
P a g e 7 5 o f
9 3
S t a t i s t i c s S c r e e n
T h i s s c r e e n i s d i s p l a y e d w h e n t h e 2 . 4 G H z S t a t i s t i c s b u t t o n o n t h e S t a t u s s c r e e n i s c l i c k e d . I t s h o w s d e t a i l s o f t h e t r a f f i c
f l o w i n g t h r o u g h t h e W i r e l e s s A c c e s s P o i n t .
Figure 71: Statistics Screen
D a t a - S t a t i s t i c s S c r e e n
System Up Time
S y s t e m U p T i m e
T h i s i n d i c a t e s h o w l o n g t h e s y s t e m h a s b e e n r u n n i n g s i n c e t h e
l a s t r e s t a r t o r r e b o o t .
2.4GHz Wireless
A u t h e n t i c a t i o n
T h e n u m b e r o f " A u t h e n t i c a t i o n " p a c k e t s r e c e i v e d . A u t h e n t i c at i o n
i s t h e p r o c e s s o f i d e n t i f i c a t i o n b e t w e e n t h e A P a n d t h e c l i e n t .
D e a u t h e n t i c a t i o n
T h e n u m b e r o f " D e a u t h e n t i c a t i o n " p a c k e t s r e c e i v e d .
D e a u t h e n t i c a t i o n i s t h e p r o c e s s o f e n d i n g a n e x i s t i n g
a u t h e nt i c a t i o n r e l a t i o n s h i p .
A s s o c i a t i o n
T h e n u m b e r o f " A s s o c i a t i o n " p a c k e t s r e c e i v e d . A s s o c i a t i o n
c r e a t e s a c o n n e c t i o n b e t w e e n t h e A P a n d t h e c l i e n t . U s u a l l y ,
c l i e n t s a s s o c ia t e w i t h o n l y o n e ( 1 ) A P a t a n y t i m e .
D i s a s s o c i a t i o n
T h e n u m b e r o f " D i s a s s o c i a t i o n " p a c k e t s r e c e i v e d . D i s a s s oc i a t i o n
b r e a k s t h e e x i s t i n g c o n n e c t i o n b e t w e e n t h e A P a n d t h e c l i e n t .
R e a s s o c i a t i o n
T h e n u m b e r o f " R e a s s o c i a t i o n " p a c k e t s r e c e i v e d . R e a s s o c i at i o n
i s t h e s e r v i c e t h a t e n a b l e s a n e s t a b l i s h e d a s s o c i a t i o n ( b e t w e e n
A P a n d c l i e n t ) t o b e t r a n s f e r r e d f r o m o n e A P t o a n o t h e r ( o r t h e
s a m e ) A P .
Wireless
M S D U
N u m b e r o f v a l i d D a t a p a c k e t s t r a n s m i t t e d t o o r r e c e i v e d f r o m
W i r e l e s s S t at i o n s , a t a p p l i c a t i o n l e v e l .
D a t a
N u m b e r o f v a l i d D a t a p a c k e t s t r a n s m i t t e d t o o r r e c e i v e d f r o m
W i r e l e s s S t at i o n s , a t d r i v e r l e v e l .
M u l t i c a s t P a c k e t s
N u m b e r o f B r o a d c a s t p a c k e t s t r a n s m i t t e d t o o r r e c e i v e d f r o m
W i r e l e s s S t at i o n s , u s i n g M u l t i c a s t t r a n s m i s s i o n .
M a n a g e m e n t
N u m b e r o f M a n a g e m e n t p a c k e t s t r a n s m i t t e d t o o r r e c e i v e d f r o m
W i r e l e s s S t at i o n s .
C o n t r o l
N u m b e r o f C o n t r o l p a c k e t s t r a n s m i t t e d t o o r r e c e i v e d f r o m
W i r el e s s S t a t i o n s .
Page 76
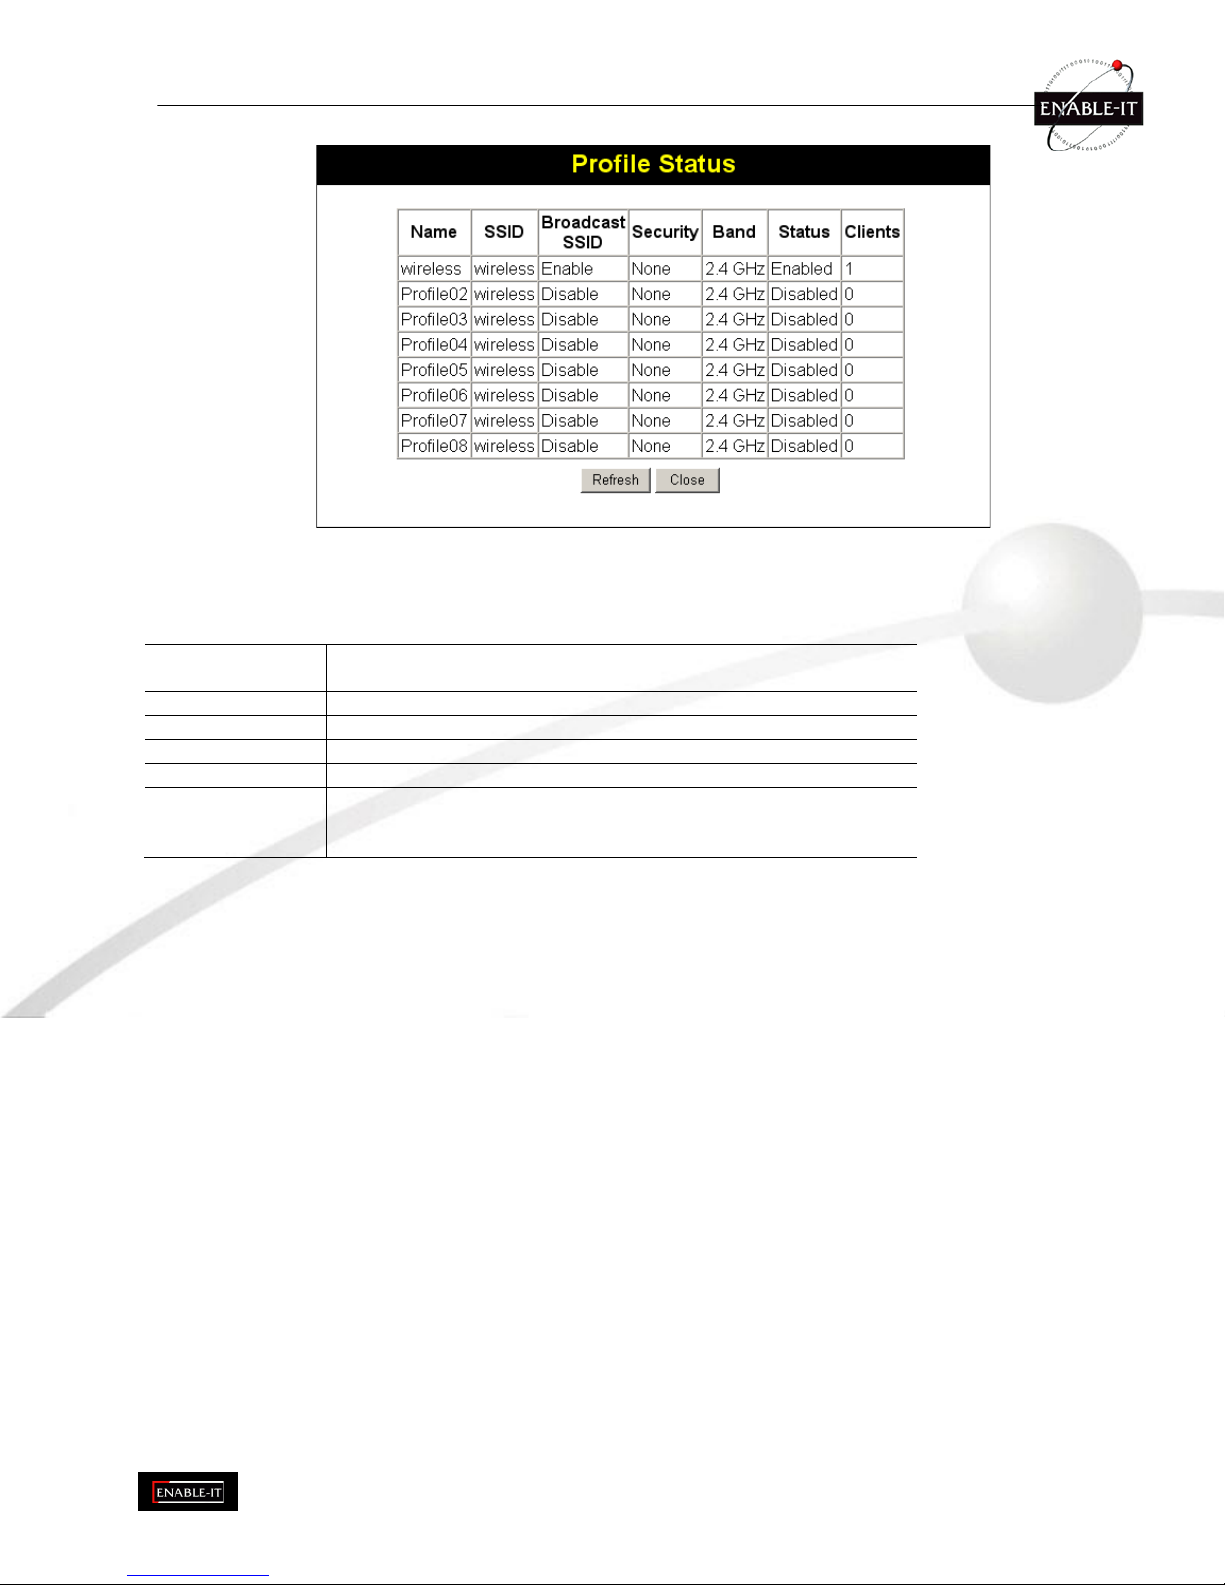
P a g e 7 6 o f
9 3
P r o f i l e S t a t u s
T h e P r o f i l e S t a t u s s c r e e n i s d i s p l a y e d w h e n t h e P r o f i l e S t a t u s b u t t o n o n t h e S t a t u s s c r e e n i s c l i c k e d .
Figure 72: Profile Screen
F o r e a c h p r o f i l e , t h e f o l l o w i n g d a t a i s d i s p l a y e d :
N a m e
T h e n a m e y o u g a v e t o t h i s p r o f i l e ; i f y o u d i d n ' t c h a n g e t h e n a m e ,
t h e d e f a u l t n a m e i s u s e d .
S S I D
T h e S S I D a s s i g n e d t o t h i s p r o f i l e .
B r o a d c a s t S S I D
I n d i c a t e s w h e t h e r o r n o t t h e S S I D i s b r o a d c a s t .
B a n d
T h e W i r e l e s s b a n d ( 2 . 4 G H z o r 5 G H z ) u s e d b y t h i s p r o f i l e .
S t a t u s
I n d i c a t e s w h e t h e r o r n o t t h i s p r o f i l e i s e n a b l e d o r c u r r e n t l y u s e d .
C l i e n t s
T h e n u m b e r o f w i r e l e s s s t a t i o n s c u r r e n t l y u s i n g a c c e s s i n g t h i s
A c c e s s P o i n t u s i n g t h i s p r o f i l e .
I f t h e p r o f i l e i s d i s a b l e d , t h i s w i l l a l w a y s b e z e r o .
Page 77
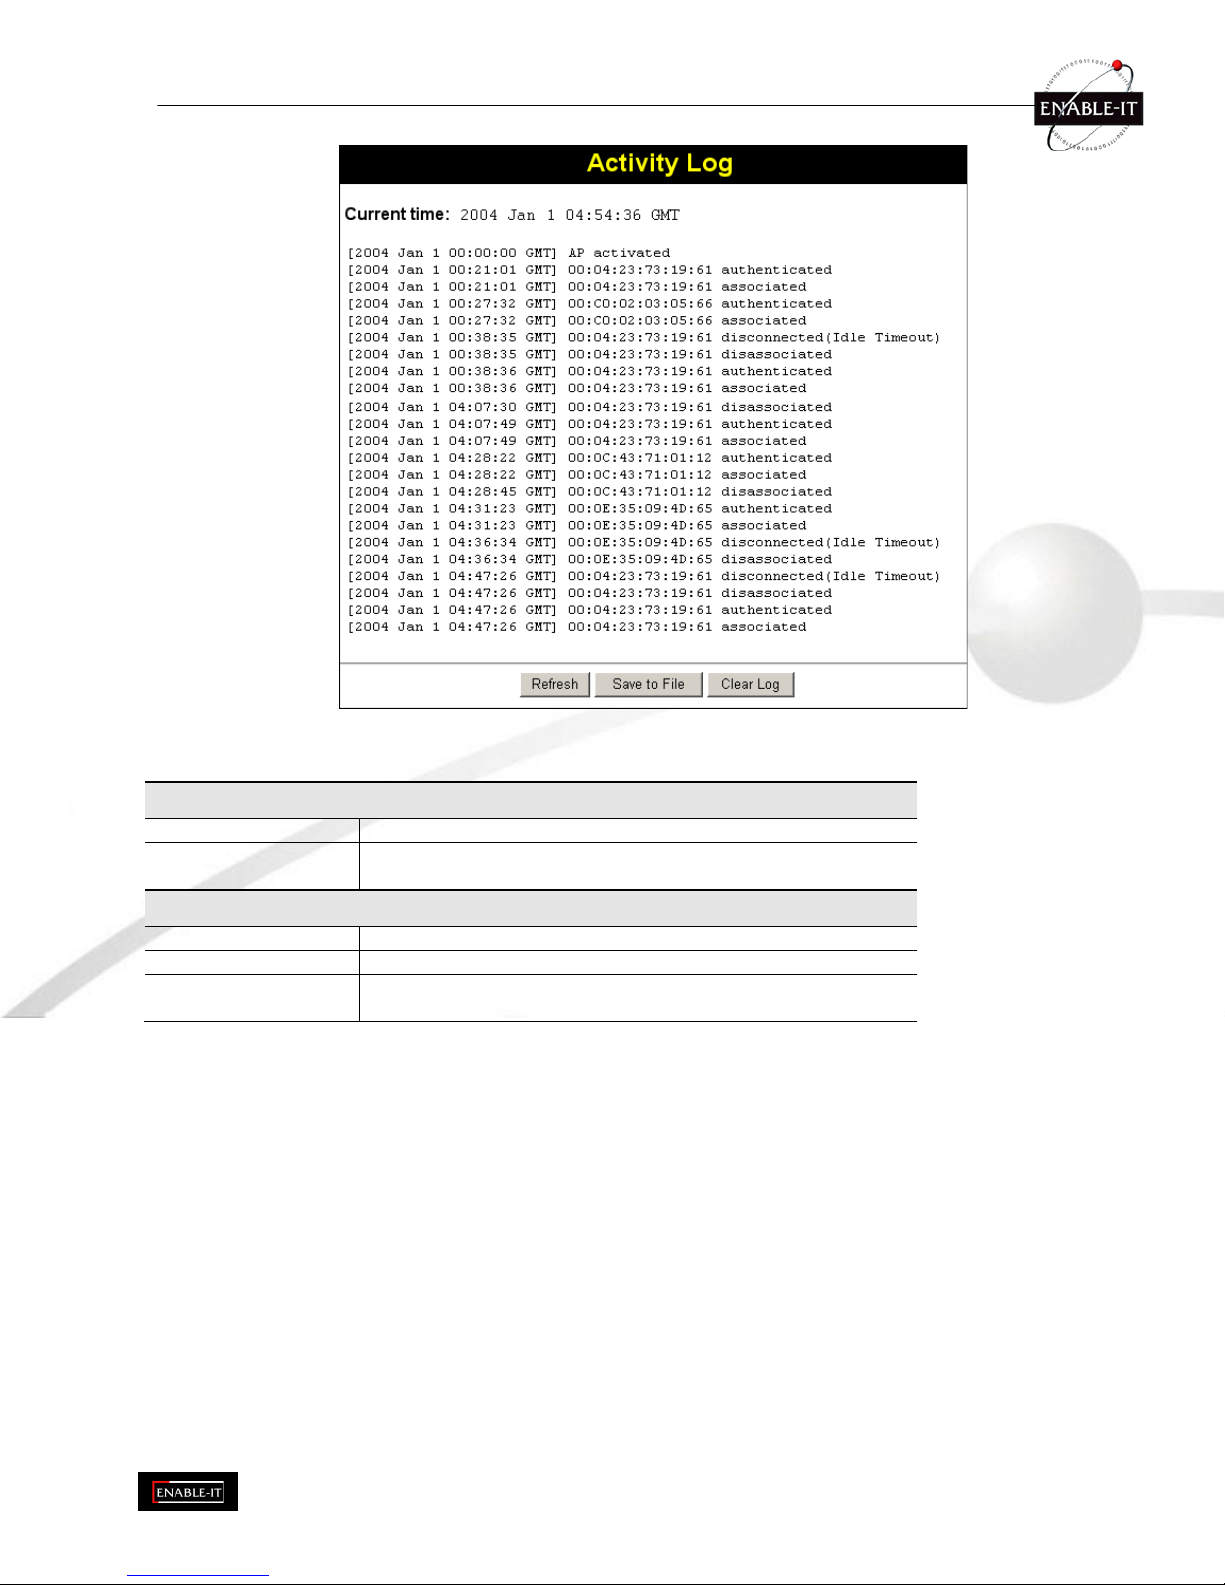
P a g e 7 7 o f
9 3
A c t i v i t y L o g
T h i s s c r e e n i s d i s p l a y e d w h e n t h e L o g b u t t o n o n t h e S t a t u s s c r e e n i s c l i c k e d .
Figure 73: Activity Log Screen
D a t a - A c t i v i t y L o g
Data
C u r r e n t T i m e
T h e s y s t e m d a t e a n d t i m e i s d i s p l a y e d .
L o g
T h e L o g s h o w s d e t a i l s o f t h e c o n n e c t i o n s t o t h e W i r e l e s s
A c c e s s P o i n t .
Buttons
R e f r e s h
U p d a t e t h e d a t a o n s c r e e n .
S a v e t o f i l e
S a v e t h e l o g t o a f i l e o n y o u r p c .
C l e a r L o g
T h i s w i l l d e l e t e a l l d a t a c u r r e n t l y i n t h e L o g . T h i s w i l l m a k e i t
e a s i e r t o r e a d n e w m e s s a g e s .
Page 78
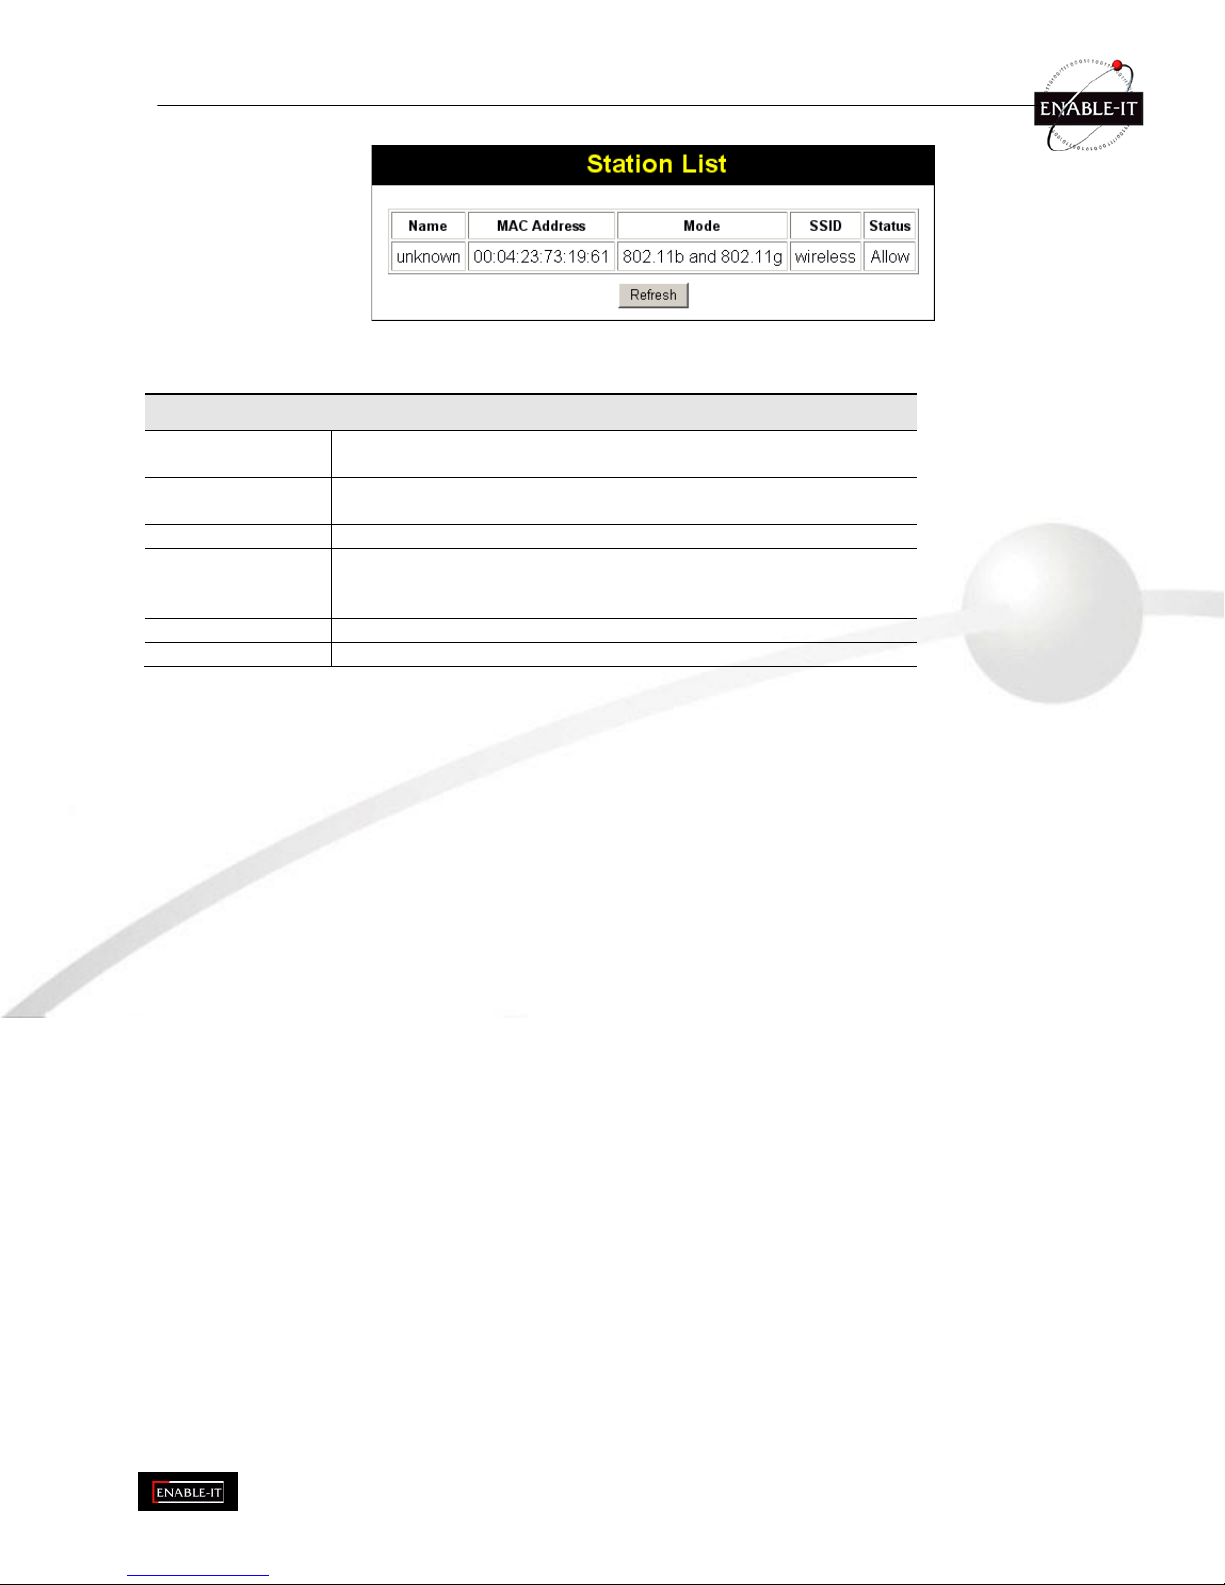
P a g e 7 8 o f
9 3
S t a t i o n L i s t
T h i s s c r e e n i s d i s p l a y e d w h e n t h e S t a t i o n s b u t t o n o n t h e S t a t u s s c r e e n i s c l i c k e d .
Figure 74 Station List Screen
D a t a - S t a t i o n L i s t S c r e e n
Station List
N a m e
T h e n a m e o f e a c h W i r e l e s s S t a t i o n i s d i s p l a y e d . I f t h e n a m e i s n o t
k n o w , " u n k n o w n " i s d i s p l a y e d f o r t h e n a m e .
M A C A d d r e s s
T h e M A C ( p h y s i c a l ) a d d r e s s o f e a c h W i r e l e s s S t a t i o n i s
d i s p l a y e d .
M o d e
T h e m o d e o f e a c h W i r e l e s s S t a t i o n .
S S I D
T h i s d i s p l a y s t h e S S I D u s e d t h e W i r e l e s s s t a t i o n . B e c a u s e t h e
W i r el e s s A c c e s s P o i n t s u p p o r t s m u l t i p l e S S I D s , d i f f e r e n t P C s
c o u l d c o n n e c t u s i n g d i f f e r e n t S S I D s .
S t a t u s
T h i s i n d i c a t e s t h e c u r r e n t s t a t u s o f e a c h W i r e l e s s S t a t i o n .
R e f r e s h B u t t o n
U p d a t e t h e d a t a o n s c r e e n .
C h a p t e r 6
A c c e s s P o i n t M a n a g e m e n t
This Chapter explains when and how to use the Wireless Access Point's "Management" Features.
O v e r v i e w
T h i s C h a p t e r c o v e r s t h e f o l l o w i n g f e a t u r e s , a v a i l a b l e o n t h e W i r e l e s s A c c e s s P o i n t ’ s M a n a g em e n t m e n u .
• Admin Login
• Auto Config/Update
• Config File
• Log Settings
• Rogue APs
• SNMP
• Upgrade Firmware
A d m i n L o g i n S c r e e n
T h e A d m i n L o g i n s c r e e n a l l o w s y o u t o a s s i g n a p a s s w o r d t o t h e W i r e l e s s A c c e s s P o i n t . T h i s p a s s w o r d l i m i t s a c c e s s t o
t h e c o n f i g u r a t i o n i n t e r f a c e . T h e d e f a u l t p a s s w o r d i s p a s s w o r d . I t i s r e c o m m e n d e d t h a t t h i s b e c h a n g e d , u s i n g t h i s
s c r e e n .
Page 79
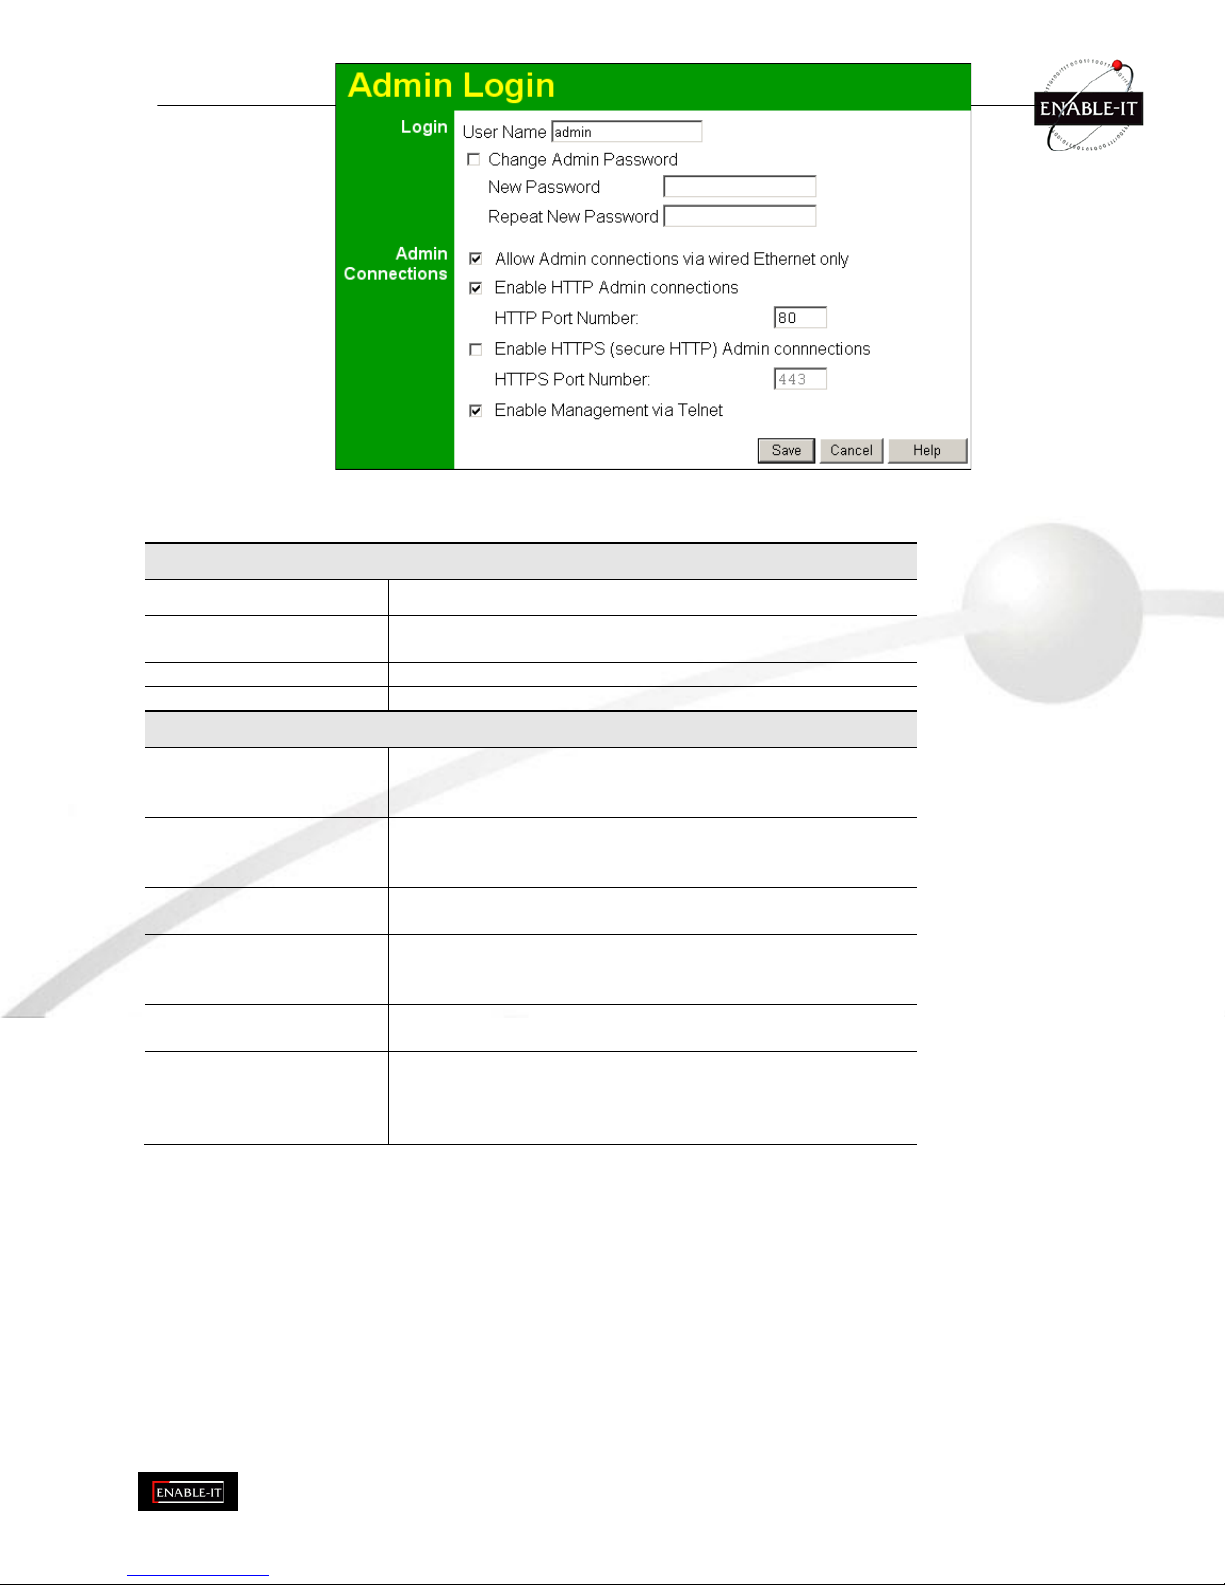
P a g e 7 9 o f
9 3
Figure 75: Admin Login Screen
D a t a - A d m i n L o g i n S c r e e n
Login
User Name
E n t e r t h e l o g i n n a m e f o r t h e A d m i n i s t r a t o r .
C h a n g e A d m i n
P a s sw o r d
I f y o u w i s h t o c h a n g e t h e A d m i n p a s s w o r d , c h e c k t h i s f i e l d
a n d e n t e r t h e n e w l o g i n p a s s w o r d i n t h e f i e l d s b e l o w .
N e w P a s s w o r d
E n t e r t h e d e s i r e d l o g i n p a s s w o r d .
R e p e a t N e w P a s s w o r d
R e -e n t e r t h e d e s i r e d l o g i n p a s s w o r d .
Admin Connections
A l l o w A d m i n
c o n n e ct i o n s v i a w i r e d
E t h e r n e t o n l y
I f c h e c k e d , t h e n A d m i n c o n n e c t i o n s v i a t h e W i r e l e s s
i n t e r f a c e w i l l n o t b e a c c e p t e d .
E n a b l e H T T P
E n a b l e t h i s t o a l l o w a d m i n c o n n e c t i o n s v i a H T T P . I f
e n a b l e d , y o u m u s t p r o v i d e a p o r t n u m b e r i n t h e f i e l d b e l o w .
E i t h e r H T T P o r H T T P S m u s t b e e n a b l e d .
H T T P P o r t N u m b e r
E n t e r t h e p o r t n u m b e r t o b e u s e d f o r H T T P c o n n e c t i o n s t o
t h i s d e v i c e . T h e d e f a u l t v a l u e i s 8 0 .
E n a b l e H T T P S
E n a b l e t h i s t o a l l o w a d m i n c o n n e c t i o n s v i a H T T P S ( s e c u r e
H T T P ) . I f e n a b l e d , y o u m u s t p r o v i d e a p o r t n u m b e r i n t h e
f i e l d b e l o w . E i t h e r H T T P o r H T T P S m u s t b e e n a b l e d .
H T T P S P o r t N u m b e r
E n t e r t h e p o r t n u m b e r t o b e u s e d f o r H T T P S c o n n e ct i o n s t o
t h i s d e v i c e . T h e d e f a u l t v a l u e i s 4 4 3 .
E n a b l e T e l n e t
I f d e s i r e d , y o u c a n e n a b l e t h i s o p t i o n . I f e n a b l e d , y o u w i l l
a b l e t o c o n n e c t t o t h i s A P u s i n g a T e l n e t c l i e n t . Y o u w i l l
h a v e t o p r o v i d e t h e s a m e l o g i n d a t a ( u s e r n a m e , p a s sw o r d )
a s f o r a H T T P ( W e b ) c o n n e c t i o n .
Page 80
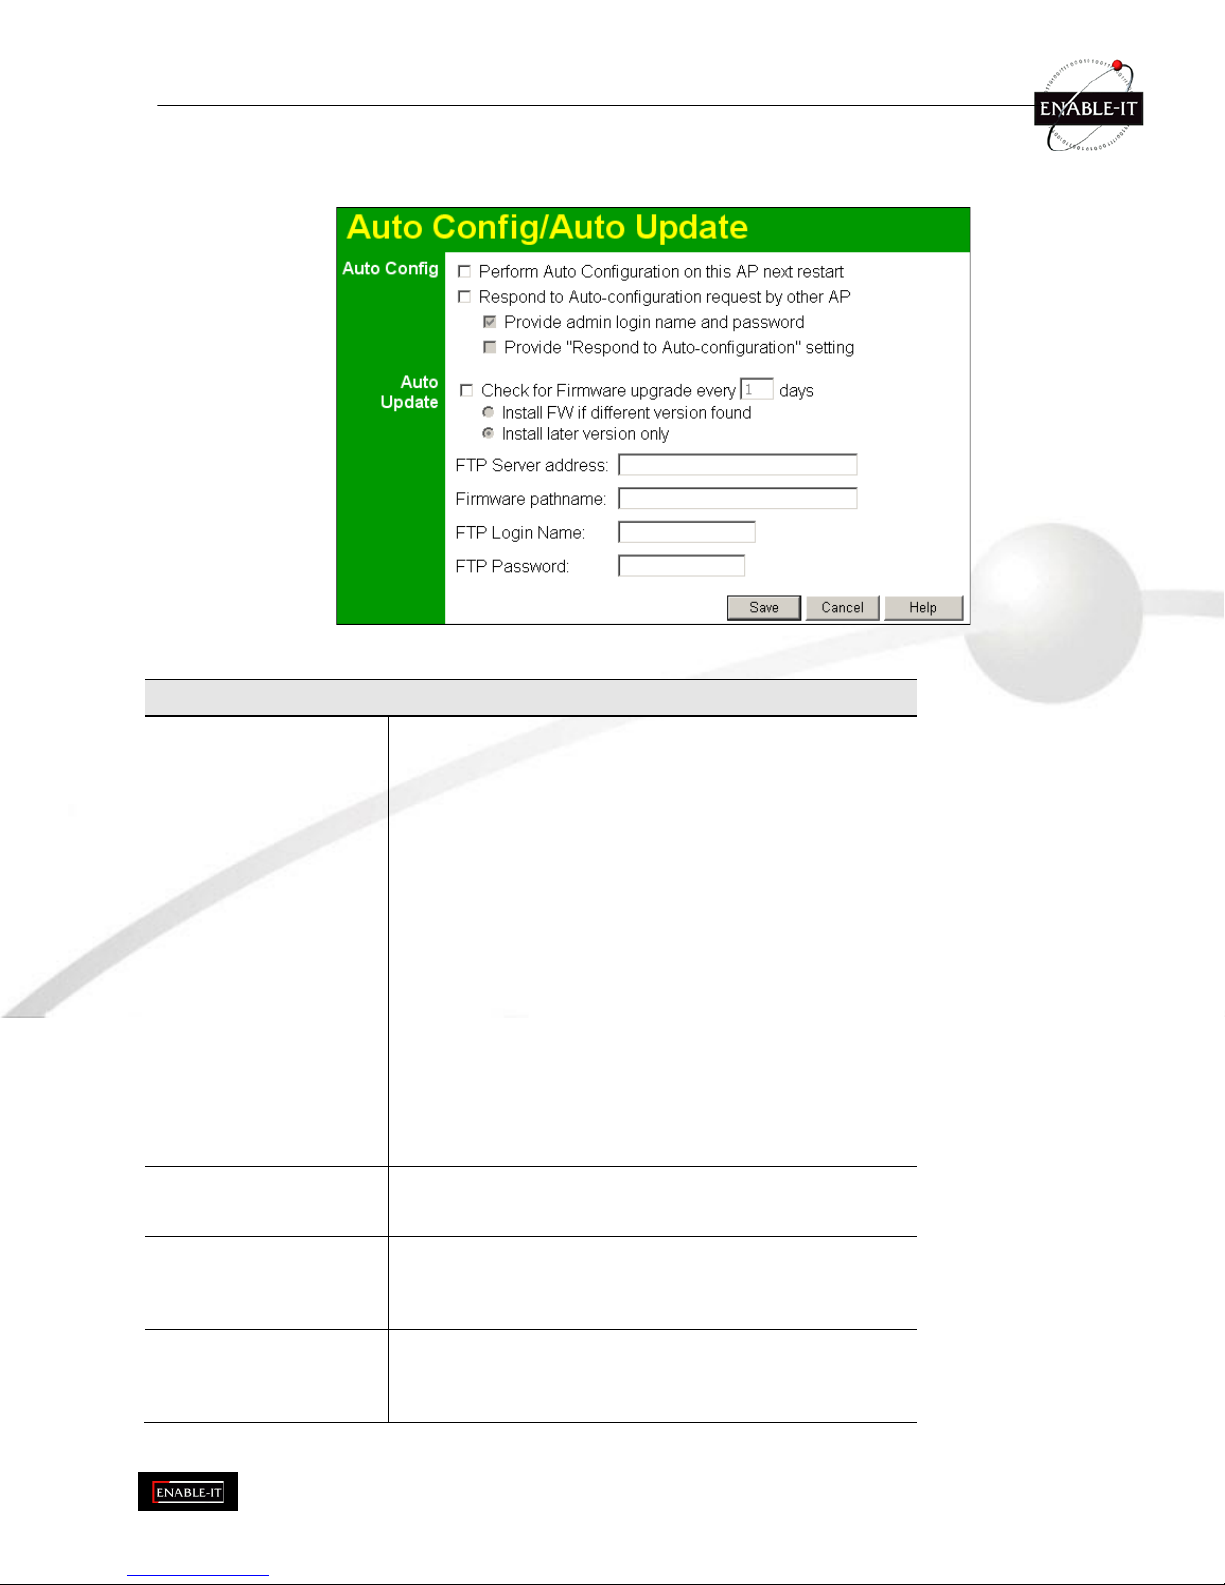
P a g e 8 0 o f
9 3
A u t o C o n f i g / U p d a t e
T h e A u t o C o n f i g / U p d a t e s c r e e n p r o v i d e s t w o ( 2 ) f e a t u r e s :
• Auto Config - The Access Point will configure itself by copying data from another (compatible) Access Point.
• Auto Update - The Access Point will update it Firmware by downloading the Firmware file from your FTP
Server.
F i g u r e 7 6 : A u t o C o n f i g / U p d a t e S c r e e n
D a t a - A u t o C o n f i g / U p d a t e S c r e e n
Admin Connections
P e r f o r m A u t o
C o n f i g urat i o n o n t h i s
A P n e x t r e s t a r t
I f c h e c k e d , t h i s A P w i l l p e r f o r m A u t o C o n f i g u r a t i o n t h e n e x t
t i m e i t r e s t a r t s .
• T h e w i r e d L A N ( N O T t h e W i r e l e s s L A N ) w i l l b e
s e a r c h e d f o r c o m p a t i b l e A P s .
• I f a c o m p a t i b l e A P i s f o u n d , i t s c o n f i g u r a t i o n i s
c o pi e d . I f m o r e t h a n o n e c o m p a t i b l e A P e x i s t s , t h e
f i r s t o n e f o u n d i s u s e d .
• S o m e d a t a c a n n o t b e c o p i e d :
o T h e I P a d d r e s s i s n o t c o p i e d , a n d w i l l n o t
c h a n g e .
o T h e o p e r a t i n g m o d e ( R e p e a t e r , B r i d g e ,
e t c ) i s n o t c o p i e d , a n d w i l l n o t c h a n g e .
Note: This checkbox is automatically disabled, so the
Auto-configuration is only performed once.
R e s p o n d t o A u t o c o n f i g u r a t i o n r e q u e s t
b y o t h e r A P
I f c h e c k e d , t h i s A P w i l l r e s p o n d t o " A u t o C o n f i g u r a t i o n "
r e q u e s t s i t r e c e i v e s . I f n o t c h e c k e d , " A u t o C o n f i g u r a t i o n "
r e q u e s t s w i l l b e i g n o r e d .
P r o v i d e l o g i n n a m e a n d
p a s s w o r d
I f e n a b l e d , t h e l o g i n n a m e a n d p a s s w o r d o n t h i s A P i s
s u pp l i e d t h e t h e A P m a k i n g t h e A u t o -c o n f i g u r a t i o n r e q u e s t .
I f d i s a b l e d , t h e A P m a k i n g t h e A u t o -c o n f i g u r a t i o n r e q u e s t
w i l l k e e p i t s e x i s t i n g l o g i n n a m e a n d p a s s w o r d .
P r o v i d e " R e s p o n d t o
A u t o -c o n f i g u r a t i o n "
s e t t i n g
I f e n a b l e d , t h e " R e s p o n d t o A u t o -c o n f i g u r a t i o n " s e t t i n g o n
t h i s A P i s s u p p l i e d t h e t h e A P m a k i n g t h e A u t o c o n f i g u r a t i o n r e q u e s t . I f d i s a b l e d , t h e A P m a k i n g t h e A u t o c o n f i g u r a t i o n r e q u e s t w i l l k e e p i t s e x i s t i n g s e t t i n g .
Page 81
P a g e 8 1 o f
9 3
Auto Update
C h e c k f o r F i r m w a r e
u p g r a d e
If enabled, this AP will check to see if a Firmw a r e ( F W )
u p g r a d e i s a v a i l a b l e o n t h e s p e c i f i e d F T P S e r v e r . I f
e n a b l e d :
• Enter the desired time interval (in days) between
checks.
• Select the desired option for installation (see next
item).
• Provide the FTP server information.
I n s t a l l . . .
S e l e c t t h e d e s i r e d o p t i o n :
• Install FW if different version found
If selected, then if the firmware file at the specified
location is different to the current installed version,
the FW will be installed. This allows "Downgrades" installing an older version of the FW to replace the
current version.
• Install later version only
If selected, then the firmware file at the specified
location will only be installed if it is a later version.
F T P S e r v e r a d d r e s s
E n t e r t h e a d d r e s s ( d o m a i n n a m e o r I P a d d r e s s ) o f t h e F T P
S e r v e r .
F i r m w a r e p a t h n a m e
E n t e r t h e f u l l p a t h ( i n c l u d i n g t h e F W f i l e n a m e ) t o t h e t h e F W
f i l e o n t h e F T P S e r v e r .
F T P L o g i n N a m e
E n t e r t h e l o g i n n a m e r e q u i r e d t o g a i n a c c e s s t o t h e F T P
Se r v e r .
F T P P a s s w o r d
E n t e r t h e p a s s w o r d f o r t h e l o g i n n a m e a b o v e .
Page 82
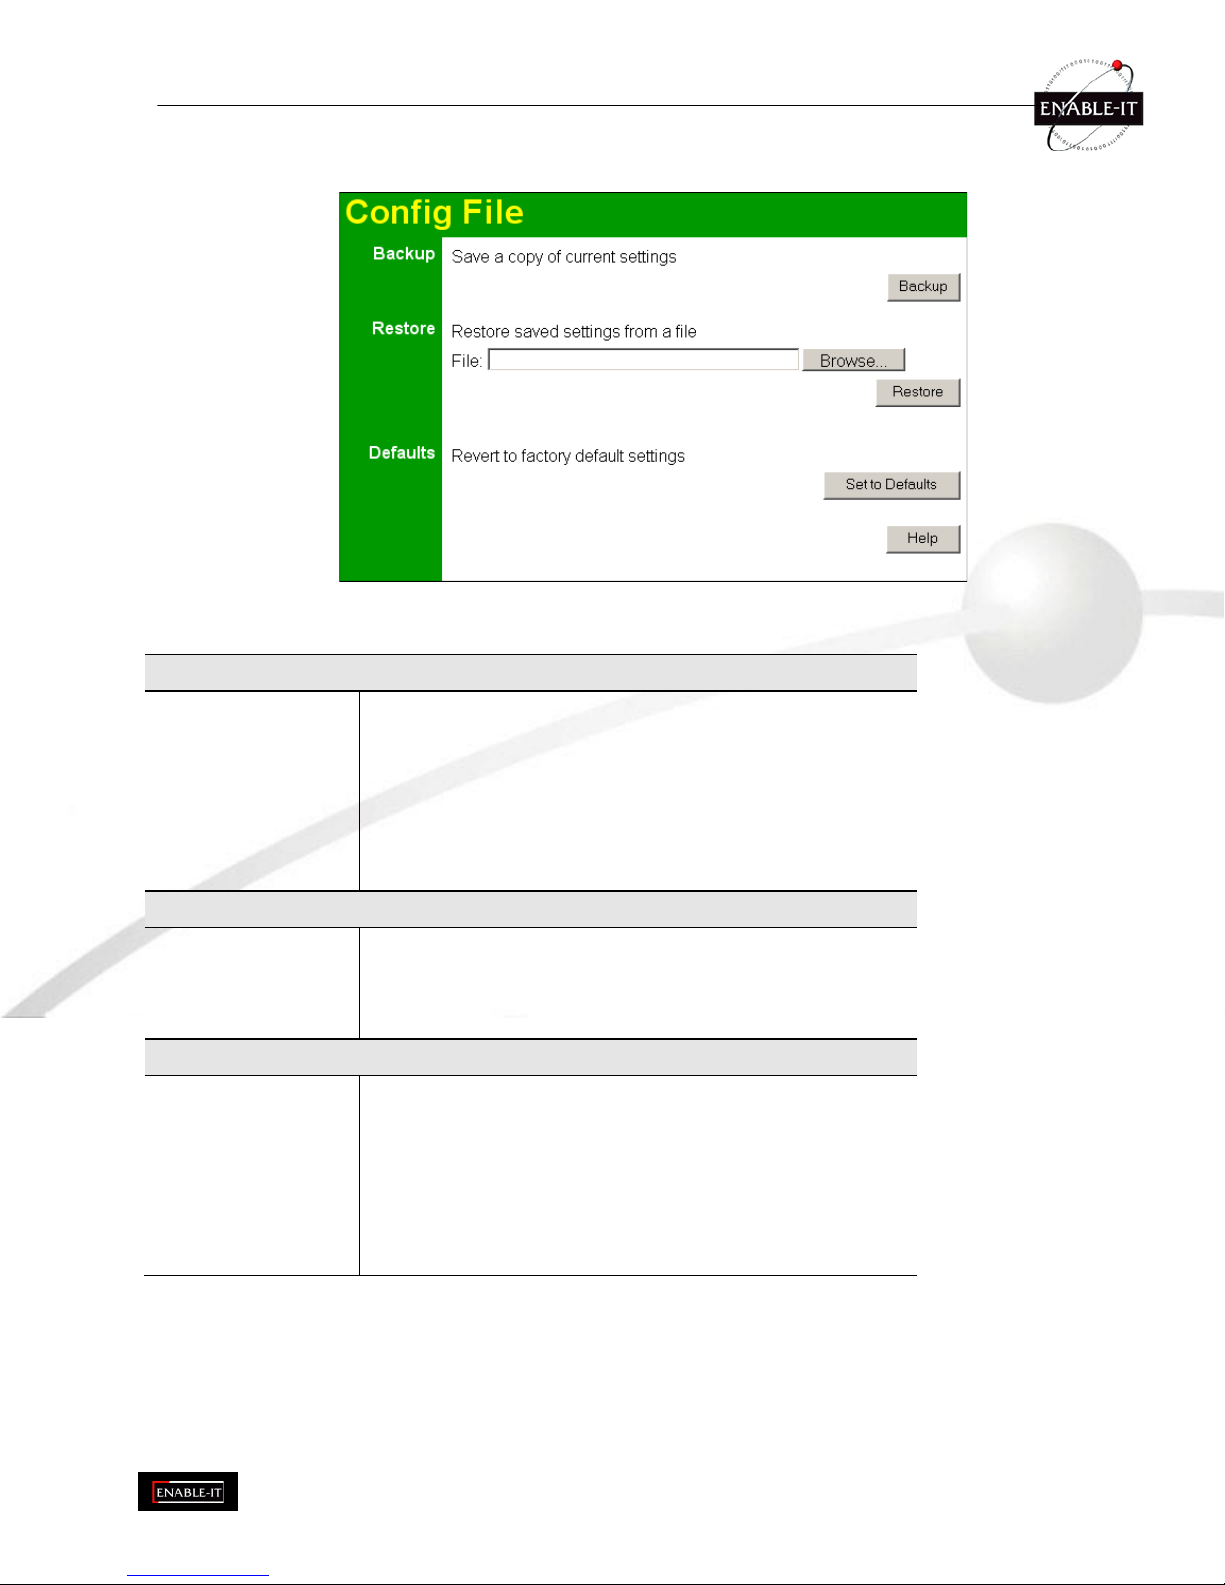
P a g e 8 2 o f
9 3
C o n f i g F i l e
T h i s s c r e e n a l l o w s y o u t o B a c k u p ( d o w n l o a d ) t h e c o n f i g u r a t i o n f i l e , a n d t o r e s t o r e ( u p l o a d ) a p r e v i o u s l y -s a v e d
c o n f i g u r a t i o n f i l e .
Y o u c a n a l s o s e t t h e W i r e l e s s A c c e s s P o i n t b a c k t o i t s f a c t o r y d e f a u l t s e t t i n g s .
T o r e a c h t h i s s c r e e n , s e l e c t C o n f i g F i l e i n t h e M a n a g e m e n t s e c t i o n o f t h e m e n u .
Figure 77: Config File Screen
D a t a - C o n f i g F i l e S c r e e n
Backup
S a v e a c o p y o f
c u rr e n t s e t t i n g s
O n c e y o u h a v e t h e A c c e s s P o i n t w o r k i n g p r o p e r l y , y o u s h o u l d
b a c k u p t h e s e t t i n g s t o a f i l e o n y o u r c o m p u t e r . Y o u c a n l a t e r
r e s t o r e t h e A c c e s s P o i n t ' s s e t t i n g s f r o m t h i s f i l e , i f n e c e s s a r y .
T o c r e a t e a b a c k u p f i l e o f t h e c u r r e n t s e t t i n g s :
• Click Back Up.
• If you don't have your browser set up to save
downloaded files automatically, locate where you want
to save the file, rename it if you like, and click S a ve .
Restore
R e s t o r e s a v e d
s e t t i n g s f r o m a f i l e
T o r e s t o r e s e t t i n g s f r o m a b a c k u p f i l e :
181. Click B r o w s e .
182. Locate and select the previously saved backup file.
183. Click Restore
Defaults
R e v e r t t o f a c t o r y
d e f a u l t s e t t i n g s
T o e r a s e t h e c u r r e n t s e t t i n g s a n d r e s t o r e t h e o r i g i n a l f a c t o r y
d e f a u l t s e t t i n g s , c l i c k S e t t o D e f a u l t s b u t t o n .
N o t e !
• This will terminate the current connection. The Access
Point will be unavailable until it has restarted.
• By default, the Access Point will act as a DHCP client,
and automatically obtain an IP address. You will need
to determine its new IP address in order to re-connect.
Page 83
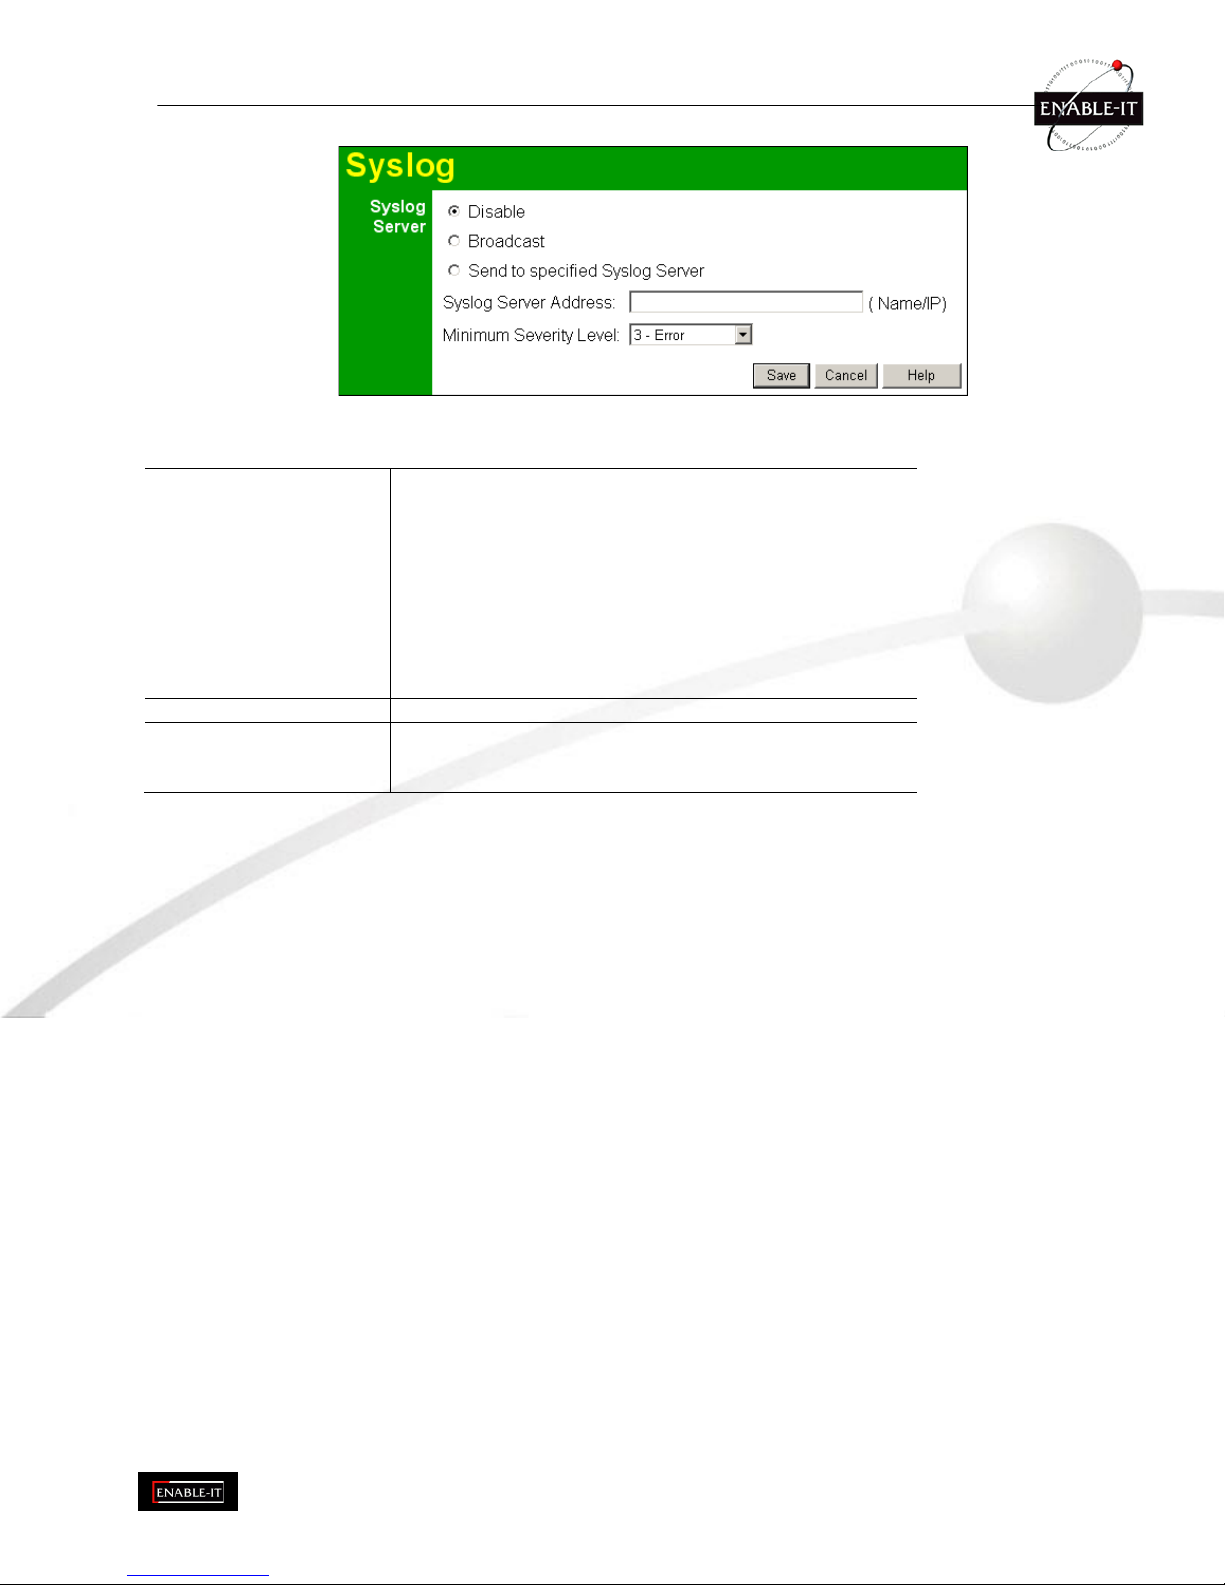
P a g e 8 3 o f
9 3
L o g S e t t i n g s ( S y s l o g )
I f y o u h a v e a S y s l o g S e r v e r o n y o u r L A N , t h i s s c r e e n a l l o w s y o u t o c o n f i g u r e t h e A c c e s s P o i n t t o s e n d l o g d a t a t o y o u r
S y s l o g S e r v e r .
Figure 78: Log Settings (Syslog) Screen
D a t a - L o g S e t t i n g s S c r e e n
S y s l o g S e r v e r
S e l e c t t h e d e s i r e d O p t i o n :
• Disable - Syslog server is not used.
• Broadcast - Syslog data is broadcast. Use this
option if different PCs act as the Syslog server at
different times.
• Send to specified Syslog Server - Select this if the
same PC is always used as the Syslog server. If
selected, you must enter the server address in the
field provided.
S y s l o g S e r v e r A d d r e s s
E n t e r t h e n a m e o r I P a d d r e s s o f y o u r S y s l o g S e r v e r .
M i n i m u m S e v e r i t y L e v e l
S e l e c t t h e d e s i r e d s e v e r i t y l e v e l . E v e n t s w i t h a s e v e r t i y l e v e l
e q u a l t o o r h i g h e r ( i . e . l o w e r n u m b e r ) t h a n t h e s e l e c t e d
l e v e l w i l l b e l o g g e d .
Page 84
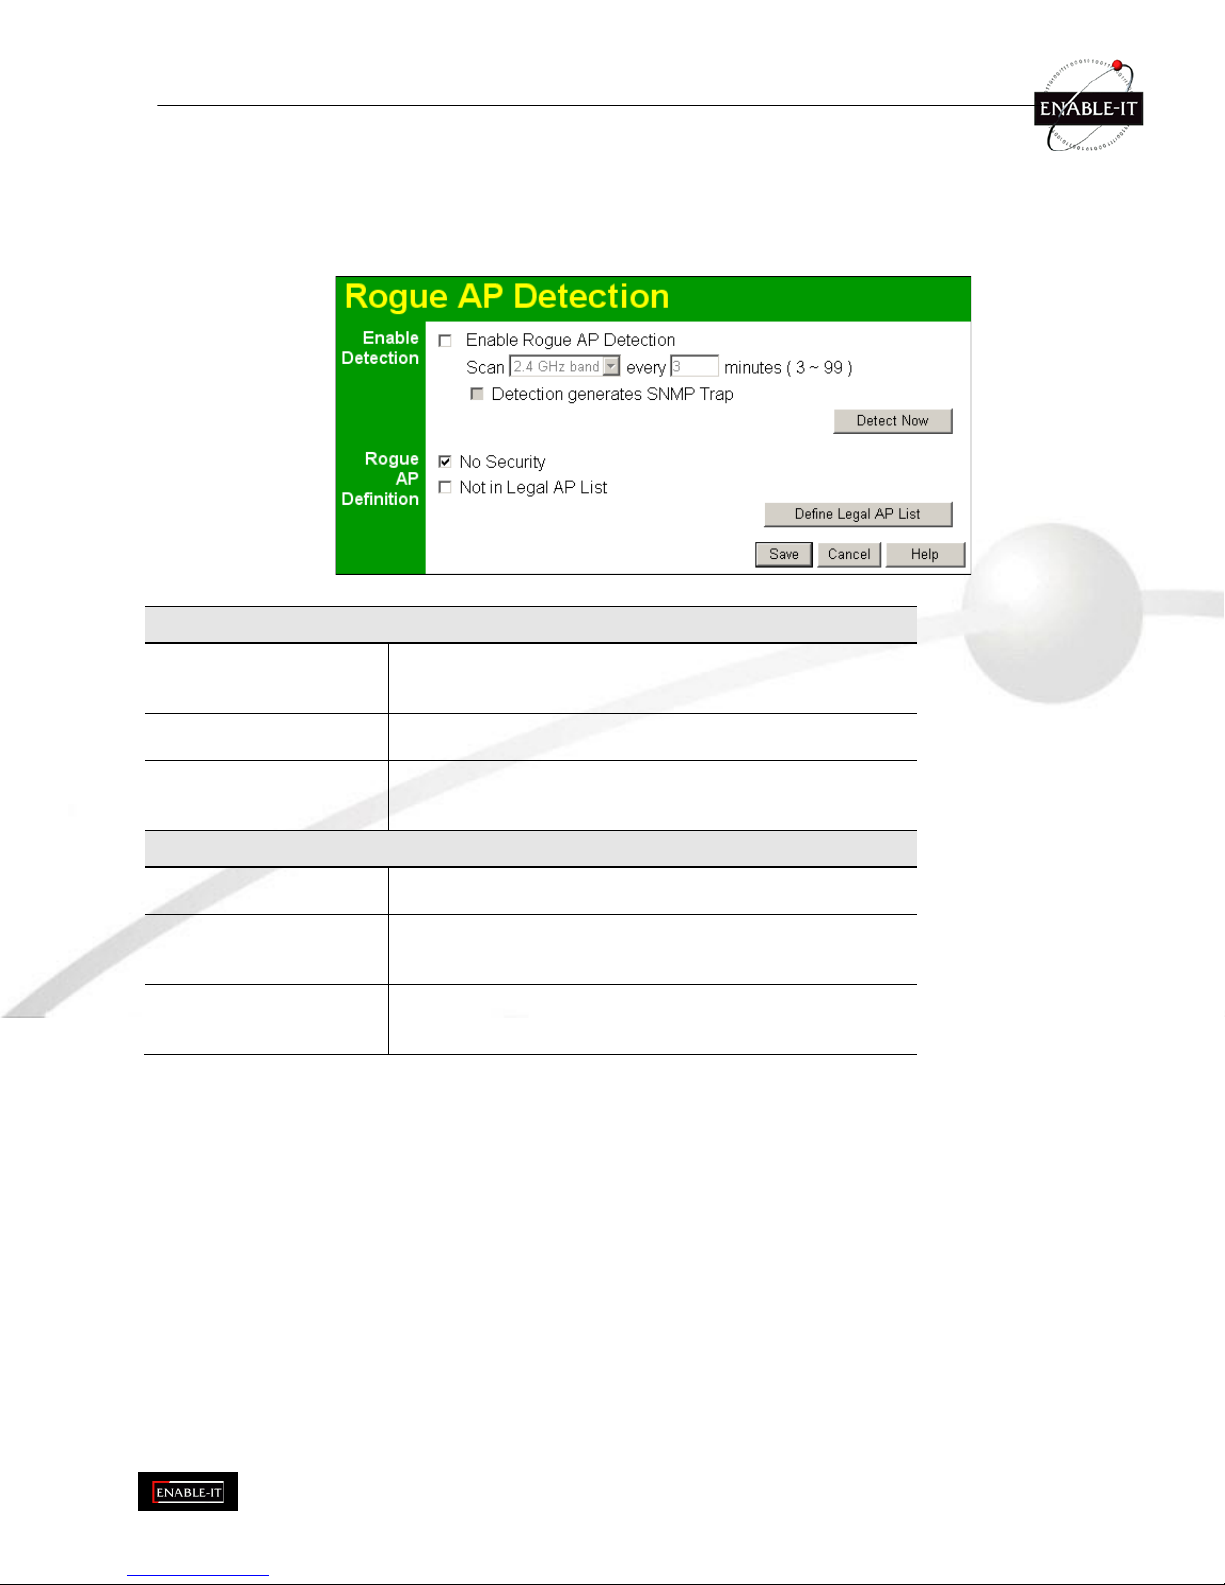
P a g e 8 4 o f
9 3
R o g u e A P s
A " R o u g e A P " i s a n A c c e s s P o i n t w h i c h s h o u l d n o t b e i n u s e , a n d s o c a n b e c o n s i de r e d t o b e p r o v i d i n g u n a u t h o r i z e d
a c c e s s t o y o u r L A N .
T h i s A c c e s s P o i n t c a n a s s i s t t o l o c a t e 2 t y p e s o f R o g u e A P s :
• APs which have Wireless security disabled.
• APs which are not in the list of valid APs which you have provided.
W h e n a R o g u e A P i s l o c a t e d , i t i s r e c o r d e d i n t h e l o g . I f u s i n g S N M P , y o u c a n a l s o c h o o s e t o h a v e d e t e c t i o n o f a R o g u e
A P g e n e r a t e a n S N M P t r a p .
F i g u r e 7 9 : R o g u e A P D e t e c t i o n S c r e e n D a t a - R o g u e A P S c r e e n
Enable Detection
E n a b l e D e t e c t i o n
T o u s e t h i s f e a t u r e , e n a b l e t h e " E n a b l e R o g u e A P
Det e c t i o n " c h e c k b o x , a n d s e l e c t t h e d e s i r e d w i r e l e s s b a n d
a n d t i m e i n t e r v a l .
S c a n
S e l e c t t h e d e s i r e d W i r e l e s s b a n d t o s c a n t o R o g u e A P s a n d
e n t e r t h e d e s i r e d t i m e i n t e r v a l b e t w e e n e a c h s c a n .
D e t e c t i o n g e n e r a t e s
S N M P T r a p
I f u s i n g S N M P , c h e c k i n g t h i s o p t i o n w i l l c a u s e a S N M P t r a p
t o b e g e n e r a t e d w h e n e v e r a R o g u e A P i s d e t e c t e d . I f n o t
u s i n g S N M P , d o n o t e n a b l e t h i s o p t i o n .
Rogue Detection
N o S e c u r i t y
I f c h e c k e d , t h e n a n y A P o p e r a t i n g w i t h s e c u r i t y d i s a b l e d i s
c o n s i d e r e d t o b e a R o g u e A P .
N o t i n L e g a l A P L i s t
I f c h e c k e d , t h e n a n y A P n o t l i s t e d i n t h e " L e g a l A P L i s t " i s
c o n s i d e r e d t o b e a R o g u e A P . I f c h e c k e d , y o u m u s t
m a i n t a i n t h e L e g a l A P L i s t .
D e f i n e L e g a l A P L i s t
C l i c k t h i s b u t t o n t o o p e n a s u b -s c r e e n w h e r e y o u c a n
m o d i f y t h e " L e g a l A P L i s t " . T h i s l i s t m u s t c o n t a i n a l l k n o w n
A P s , s o m u s t b e k e p t u p t o d a t e .
Page 85
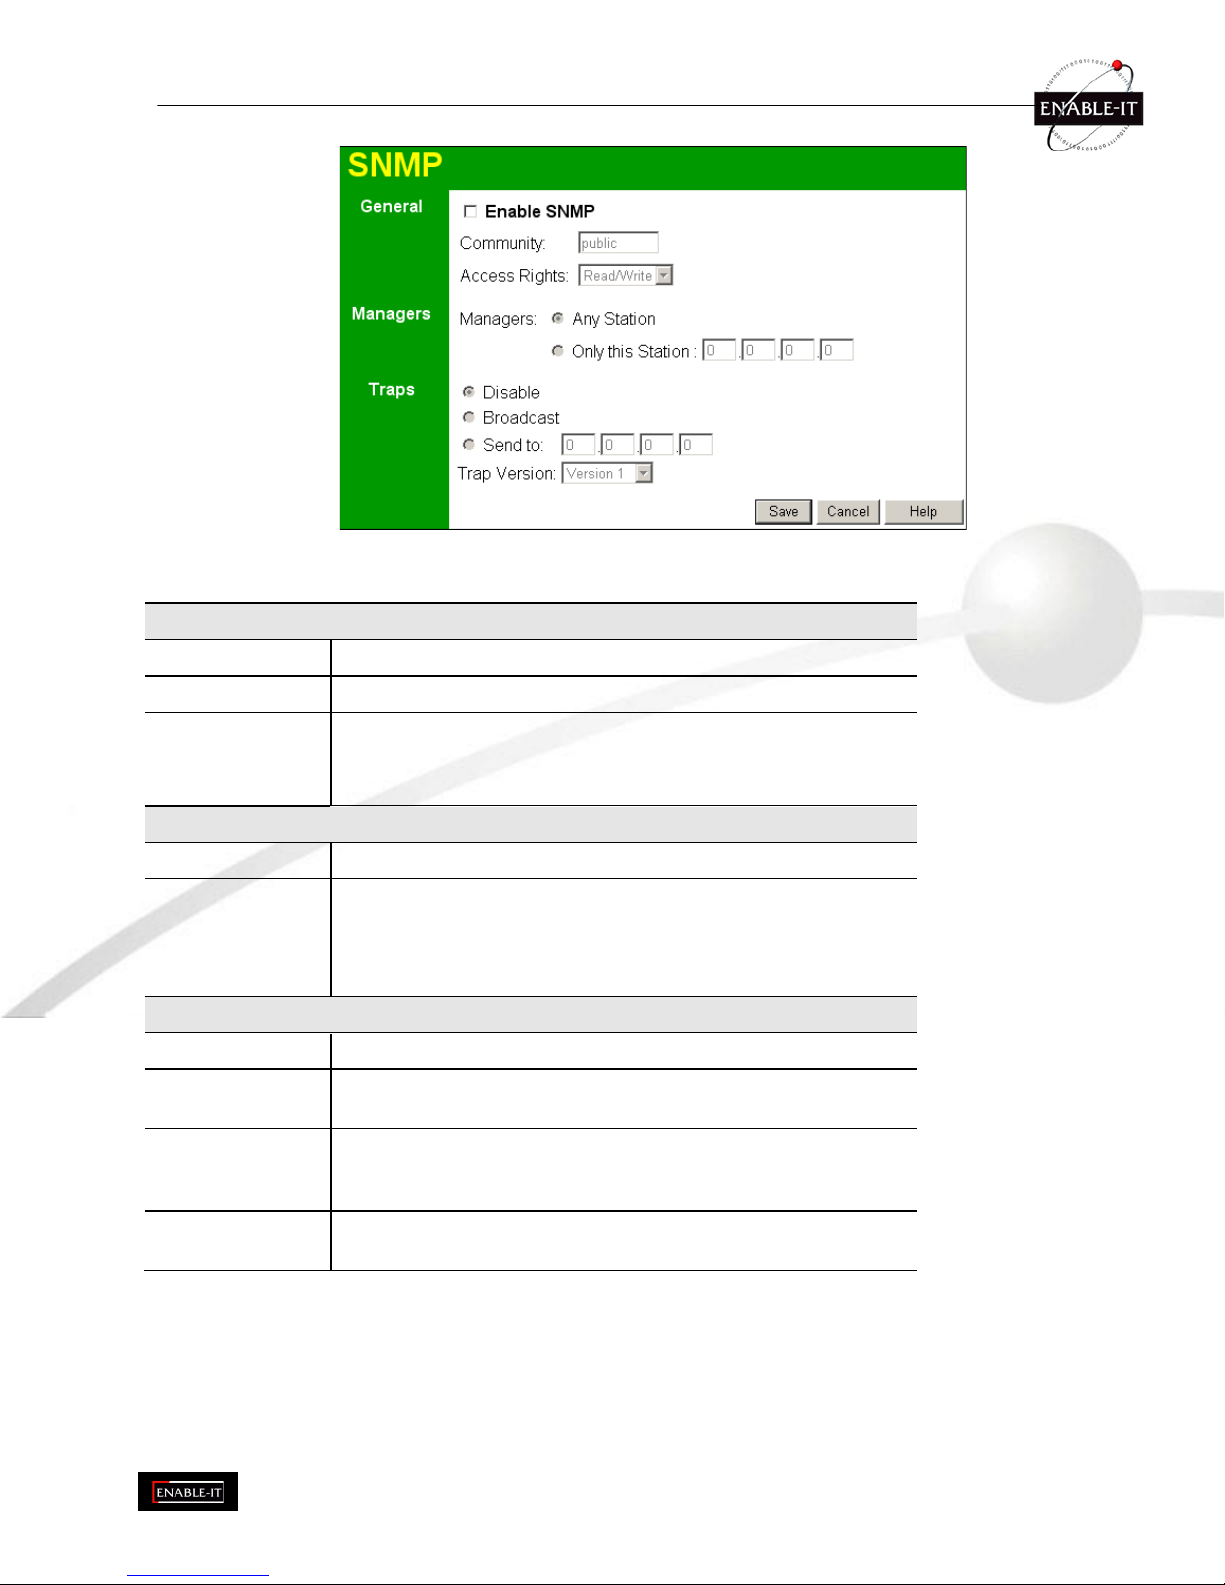
P a g e 8 5 o f
9 3
S N M P
S N M P ( S i m p l e N e t w o r k M a n a g e m e n t P r o t o c o l ) i s o n l y u s e f u l i f y o u h a v e a S N M P p r o g r a m o n y o u r P C . T o r e a c h t h i s
s c r e e n , s e l e c t S N M P i n t h e M a n a g e m e n t s e c t i o n o f t h e m e n u .
Figure 80: SNMP Screen
D a t a - S N M P S c r e e n
General
E n a b l e S N M P
Use this to enable or disable SNMP as required
C o m m u n i t y
Enter the community string, usually either "Public" or "Private".
A c c e s s R i g h t s
Select the desired option:
• Read-only - Data can be read, but not changed.
• Read/Write - Data can be read, and setting changed.
Managers
A n y S t a t i o n
The IP address of the manager station is not checked.
O n l y t h i s s t a t i o n
The IP address is checked, and must match the address you
enter in the IP address field provided.
If selected, you must enter the IP address of the required
station.
Traps
D i s a b l e
Traps are not used.
B r o a d c a s t
Select this to have Traps broadcast on your network. This
makes them available to any PC.
S e n d t o
Select this to have Trap messages sent to the specified PC
only. If selected, you must enter the IP Address of the desired
PC.
T r a p v e r s i o n
Select the desired option, as supported by your SNMP
Management program.
Page 86
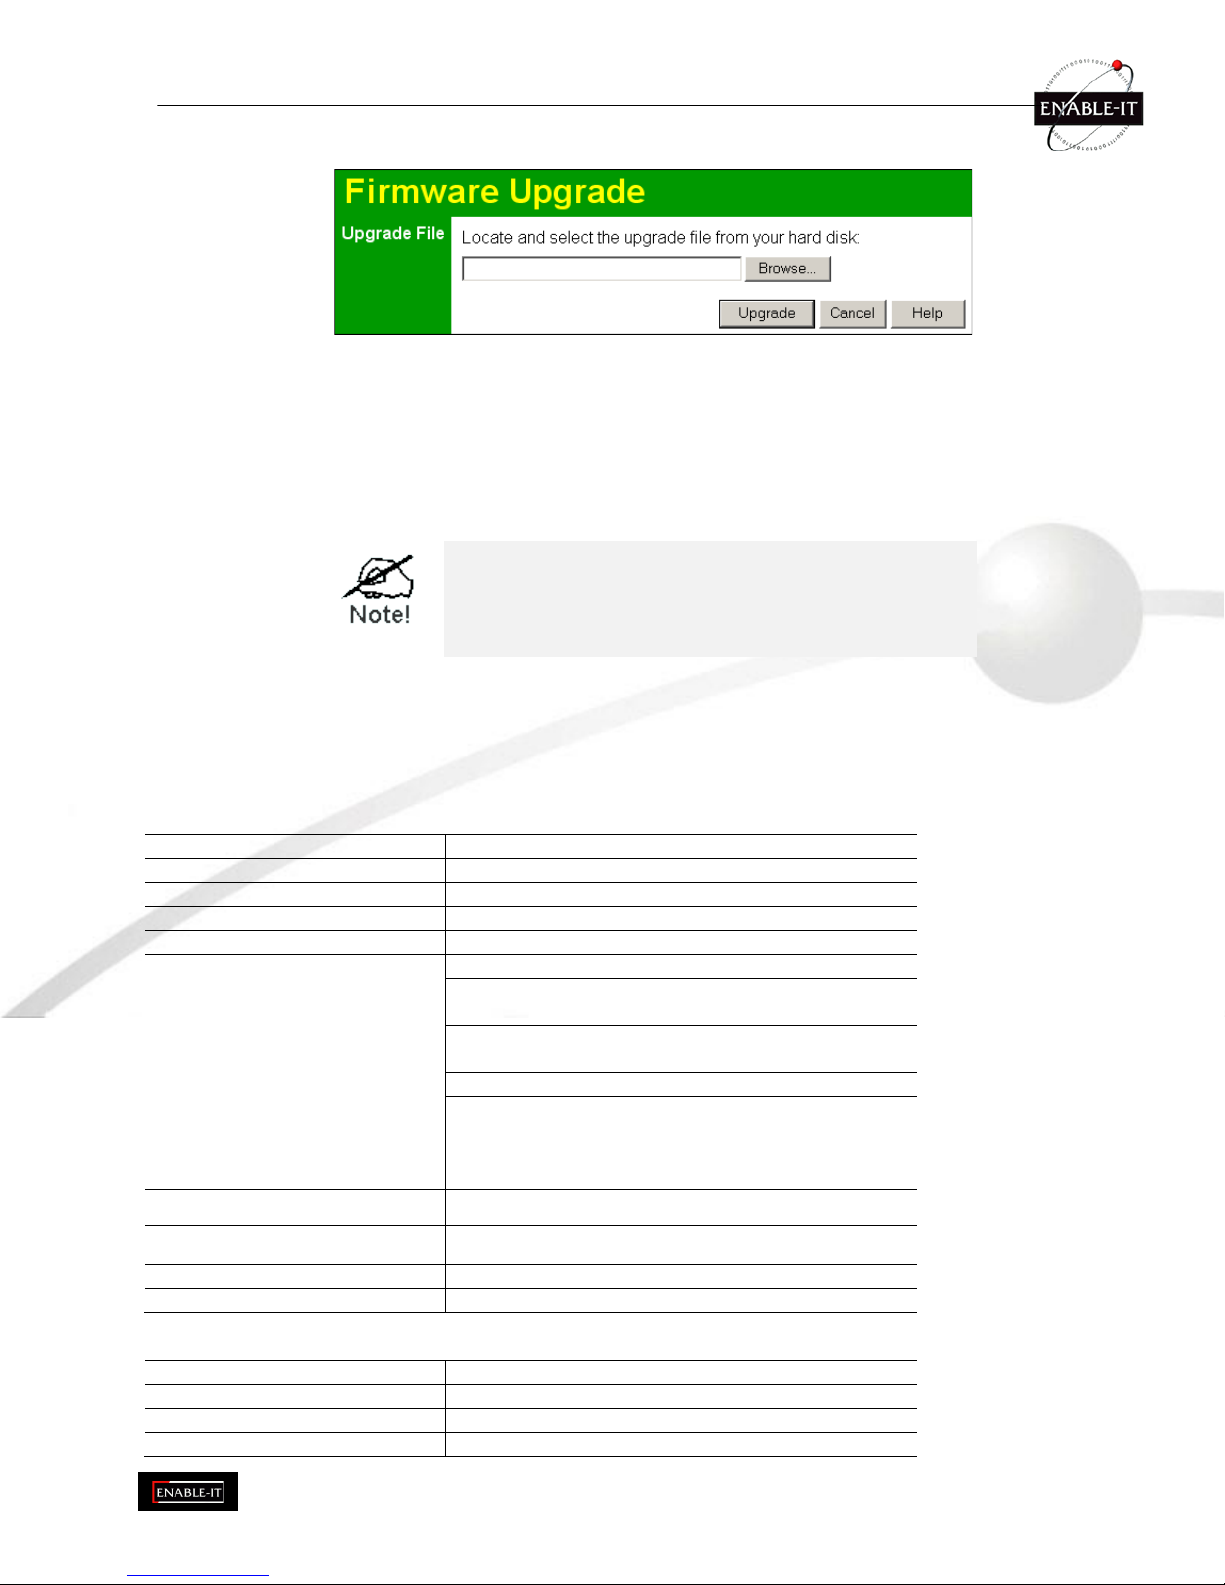
P a g e 8 6 o f
9 3
U p g r a d e F i r m w a r e
T h e f i r m w a r e ( s o f t w a r e ) i n t h e W i r e l e s s A c c e s s P o i n t c a n b e u p g r a d e d u s i n g y o u r W e b B r o w s e r .
Y o u m u s t f i r s t d o w n l o a d t h e u p g r a d e f i l e , a n d t h e n s e l e c t U p g r a d e F i r m w a r e i n t h e M a n a g em e n t s e c t i o n o f t h e m e n u .
Y o u w i l l s e e a s c r e e n l i k e t h e f o l l o w i n g .
Figure 81: Firmware Upgrade Screen
To perform the Firmware Upgrade:
184. Click the Browse button and navigate to the location of the upgrade file.
185. Select the upgrade file. Its name will appear in the Upgrade File field.
186. Click the Upgrade button to commence the firmware upgrade.
The Wireless Access Point is unavailable during the
upgrade process, and must restart when the upgrade
is completed. Any connections to or through the
Wireless Access Point will be lost.
A p p e n d i x A
S p e c i f i c a t i o n s
W i r e l e s s A c c e s s P o i n t
H a r d w a r e S p e c i f i c a t i o n s
C P U
A R 2 3 1 2
R a d i o -o n -C h i p
A R 2 1 1 2
D R A M
8 M b y t e s
F l a s h R O M
2 M b y t e s
L A N p o r t
1 x A u t o -M D I X R J 4 5 f o r 1 0 / 1 0 0 M b p s E t h e r n e t
W i r e l e s s I n t e r f a c e
E m b e d d e d A t h e r o s s o l u t i o n
N e t w o r k S t a n d a r d I E E E 8 0 2 . 1 1 b ( W i -F i ™ ) a n d I E E E
8 0 2 . 1 1 g c o m p l i a n c e
O F D M ; 8 0 2 . 1 1 b : C C K ( 1 1 M b p s , 5 . 5 M b p s ) , D Q P S K
( 2 M b p s ) , D B P S K ( 1 M b p s )
O p e r a t i n g F r e q u e n c i e s 2 . 4 1 2 . 2 . 4 9 7 G H z
O p e r a t i n g C h a n n e l s 8 0 2 . 1 1 g : 1 3 f o r N o r t h A m e r i c a , 1 3
f o r E u r o p e ( E T S I ) , 1 4 f o r J a p a n
8 0 2 . 1 1 b : 1 1 f o r N o r t h A m e r i c a , 1 4 f o r J a p a n , 1 3 f o r
E u r o p e ( E T S I )
O p e r a t i n g t e m p e r a t u r e
0 ~ 5 5 ℃
S t o r a g e t e m p e r a t u r e
-2 0
℃~ 7 0 ℃
P o w e r A d a p t e r
2 4 V D C 5 0 0 m a
D i m e n s i o n s
1 4 1 m m ( W ) x 1 0 0 m m ( D ) x 2 7 m m ( H )
W i r e l e s s S p e c i f i c a t i o n s
R e c e i v e S e n s i t i v i t y a t 1 1 M b p s
m i n . -8 5 d B m
R e c e i v e S e n s i t i v i t y a t 5 . 5 M b p s
m i n . -8 9 d B m
R e c e i v e S e n s i t i v i t y a t 2 M b p s
m i n . -9 0 d B m
R e c e i v e S e n s i t i v i t y a t 1 M b p s
m i n . -9 3 d B m
Page 87
P a g e 8 7 o f
9 3
M a x i m u m R e c e i v e L e v e l
m i n . -5 d B m
T r a n s m i t P o w e r
1 8 d B m
M o d u l a t i o n
D i r e c t S e q u e n c e S p r e a d S p e c t r u m B P S K / Q P S K /
C C K
T h r o u g h p u t
U p t o 1 9 M b p s
O p e r a t i n g R a n g e
I n d o o r s
• 30 Meters (100ft.) @ 11Mbps
• 50 Meters (165ft.) @ 5.5Mbps
• 70 Meters (230ft.) @ 2Mbps
• 9 1Meters (300ft.) @ 1Mbps
O u t d o o r s
• 152 Meters (500ft.) @ 11Mbps
• 270 Meters (885ft.) @ 5.5Mbps
• 396 Meters (1300ft.) @ 2 Mbps
• 457 Meters (1500ft.) @ 1 Mbps
S o f t w a r e S p e c i f i c a t i o n s
Feature
Details
W i r e l e s s
• Access point support
• Roaming supported
• IEEE 802.11g/11b compliance
• Supper G (up to 108Mbps)
• Auto Sensing Open System / Share Key authentication
• Wireless Channels Support
• Automatic Wireless Channel Selection
• Antenna selection
• Tx Power Adjustment
• Country Selection
• Preamble Type: long or short support
• RTS Threshold Adjustment
• Fragmentation Threshold Adjustment
• Beacon Interval Adjustment
• SSID assignment
O p e r a t i o n M o d e
• Common AP, Client/Repeater AP
• Peer-to-Peer Bridge, Point-to-Multi-Point Bridge
B r i d g e m o d e c a n b e u s e d s i m u l t a n e o u s l y w i t h C o m m o n A P m o de.
S e c u r i t y
• Open, shared, WPA, and WPA-PSK authentication
• 802.1x support
• EAP-TLS, EAP-TTLS, PEAP
• Block inter-wireless station communication
• Block SSID broadcast
M a n a g e m e n t
• Web based configuration
• RADIUS Accounting
• RADIUS-On feature
• RADIUS Accounting update
• CLI
• Message Log
• Access Control list file support
Page 88
P a g e 8 8 o f
9 3
• Configuration file Backup/Restore
• Statistics support
• Device discovery program
• Windows Utility
O t h e r F e a t u r e s
• DHCP client
• WINS client
F i r m w a r e U pg r a d e
H T T P , F T P n e t w o r k p r o t o c o l d o w n l o a d
Page 89
P a g e 8 9 o f
9 3
F C C S t a t e m e n t
T h i s e q u i p m e n t h a s b e e n t e s t e d a n d f o u n d t o c o m p l y w i t h t h e l i m i t s f o r a C l a s s B d i g i t a l d e v i c e , p u r s u a n t t o P a r t 1 5 o f
t h e F C C R u l e s . T h e s e l i m i t s a r e d e s i g n e d t o p r o v i d e r e a s o n a b l e p r o t e ct i o n a g a i n s t h a r m f u l i n t e r f e r e n c e i n a r e s i d e n t i a l
i n s t a l l a t i o n .
T h i s e q u i p m e n t g e n e r a t e s , u s e s a n d c a n r a d i a t e r a d i o f r e q u e n c y e n e r g y a n d , i f n o t i n s t a l l e d a n d u s e d i n a c c o r d a n c e
w i t h t h e i n s t r u c t i o n s , m a y c a u s e h a r m f u l i n t e r f e r e n c e t o r a d i o c o m m u n i c at i o n s . H o w e v e r , t h e r e i s n o g u a r a n t e e t h a t
i n t e r f e r e n c e w i l l n o t o c c u r i n a p a r t i c u l a r i n s t a l l a t i o n . I f t h i s e q u i p m e n t d o e s c a u s e h a r m f u l i n t e r f e r e n c e t o r a d i o o r
t e l e v i s i o n r e c e p t i o n , w h i c h c a n b e d e t e r m i n e d b y t u r n i n g t h e e q u i p m e n t o f f a n d o n , t h e u s e r i s e n c o u r a g e d t o t r y t o
c o r r e c t t h e i n t e r f e r e n c e b y o n e o f t h e f o l l o w i n g m e a s u r e s :
• Reorient or relocate the receiving antenna.
• Increase the separation between the equipment and receiver.
• Connect the equipment into an outlet on a circuit different from that to which the receiver is connected.
• Consult the dealer or an experienced radio/TV technician for help.
T o a s s u r e c o n t i n u e d c o m p l i a n c e , a n y c h a n g e s o r m o d i f i c a t i o n s n o t e x p r e s s l y a pp r o v e d b y t h e p a r t y r e s p o n s i b l e f o r
c o m p l i a n c e c o u l d v o i d t h e u s e r ' s a u t h o r i t y t o o p e r a t e t h i s e q u i p m e n t . ( E x a m p l e - u s e o n l y s h i e l d e d i n t e r f a c e c a b l e s
w h e n c o n n e c ti n g t o c o m p u t e r o r p e r i p h e r a l d e v i c e s ) .
FCC Radiation Exposure Statement
T h i s e q u i p m e n t c o m p l i e s w i t h F C C R F r a d i a t i o n e x p o s u r e l i m i t s s e t f o r t h f o r a n u n c o nt r o l l e d e n v i r o n m e n t . T h i s
e q u i p m e n t s h o u l d b e i n s t a l l e d a n d o p e r a t e d w i t h a m i n i m u m d i s t a n c e o f 2 0 c e n t i m e t e r s b e t w e e n t h e r a d i a t o r a n d y o u r
b o d y .
T h i s d e v i c e c o m p l i e s w i t h P a r t 1 5 o f t h e F C C R u l e s . O p e r a t i o n i s s u b j e c t t o t h e f o l l o wi n g t w o c o n d i t i o n s :
( 1 ) T h i s d e v i c e m a y n o t c a u s e h a r m f u l i n t e r f e r e n c e , a n d
( 2 ) t h i s d e v i c e m u s t a c c e p t a n y i n t e r f e r e n c e r e c e i v e d , i n c l u d i n g i n t e r f e r e n c e t h a t m a y c a u s e u n d e s i r e d o p e r a t i o n .
T h i s t r a n s m i t t e r m u s t n o t b e c o -l o c a t e d o r o p e r a t i n g i n c o n j u n c t i o n w i t h a n y o t h e r a n t e n n a o r t r a n s m i t t e r .
A p p e n d i x B
T r o u b l e s h o o ti n g
O v e r v i e w
T h i s c h a p t e r c o v e r s s o m e c o m m o n p r o b l e m s t h a t m a y b e e n c o u n t e r e d w h i l e u s i n g t h e W i r e l e s s A c c e s s P o i n t a n d s o m e
p o s s i b l e s o l u t i o n s t o t h e m . I f y o u f o l l o w t h e s u gg e s t e d s t e p s a n d t h e W i r e l e s s A c c e s s P o i n t s t i l l d o e s n o t f u n c t i o n
p r o pe r l y , c o n t a c t y o u r d e a l e r f o r f u r t h e r a d v i c e .
G e n e r a l P r o b l e m s
P r o b l e m 1 :
C a n ' t c o n n e c t t o t h e W i r e l e s s A c c e s s P o i n t t o c o n f i gu r e i t .
S o l u t i o n 1 :
C h e c k t h e f o l l o w i n g :
• The Wireless Access Point is properly installed, LAN connections
are OK, and it is powered ON. Check the LEDs for port status.
• Ensure that your PC and the Wireless Access Point are on the
same network segment. (If you don't have a router, this must be
the case.)
• If your PC is set to "Obtain an IP Address automatically" (DHCP
client), restart it.
• You can use the following method to determine the IP address of
the Wireless Access Point, and then try to connect using the IP
address, instead of the name.
T o F i n d t h e A c c e s s P o i n t ' s I P A d d r e s s
187. Open a MS-DOS Prompt or Command Prompt Window.
188. Use the Ping command to “ping” the Wireless Access Point.
Enter ping followed by the Default Name of the Wireless Access
Point.
e.g.
p i n g S C 0 0 3 3 1 8
189. Check the output of the ping command to determine the IP
Page 90
P a g e 9 0 o f
9 3
address of the Wireless Access Point, as shown below.
Figure 82: Ping
I f y o u r P C u s e s a F i x e d ( S t a t i c ) I P a d d r e s s , e n s u r e t h a t i t i s u s i n g a n I P
A d d r e s s w h i c h i s c o m p a t i b l e w i t h t h e W i r e l e s s A c c e s s P o i n t . ( I f n o D H C P
S e r v e r i s f o u n d , t h e W i r e l e s s A c c e s s P o i n t w i l l d e f a u l t t o a n I P A d d r e s s
a n d M a s k o f 1 9 2 . 1 6 8 . 0 . 2 2 8 a n d 2 5 5 . 2 5 5 . 2 5 5 . 0 . ) O n W i nd o w s P C s , y o u
c a n u s e C o n t r o l P a n e l -N e t w o r k t o c h e c k t h e P r o p e r t i e s f o r t h e T C P / I P
p r o t oc o l .
P r o b l e m 2 :
M y P C c a n ' t c o n n e c t t o t h e L A N v i a t h e W i r e l e s s A c c e s s P o i n t .
S o l u t i o n 2
C h e c k t h e f o l l o w i n g :
• The SSID and WEP settings on the PC match the settings on the
Wireless Access Point.
• On the PC, the wireless mode is set to "Infrastructure"
• If using the Access Control feature, the PC's name and address
is in the Trusted Stations list.
• If using 802.1x mode, ensure the PC's 802.1x software is
configured correctly. See Chapter 4 for details of setup for the
Windows XP 802.1x client. If using a different client, refer to the
vendor's documentation.
Technical Support
Enable-IT OEM Technical Support is available directly to registered distributors and
prospective customers.
Online Technical Services
Enable-IT, Inc. Technical Support is available via e-mail at [email protected]
World Wide Web Site
Enable-IT, Inc. Technical Support is available via the Internet at
http://www.ethernetextender.com/contact_us.php
Returning Products for Warranty Repair
E n a b l e -I T , I n c . w a r r a n t s t o t h e o r i g i n a l p u r c h a s e r o f t h e P r o d u c t ( " y o u " o r t h e " E n d U s e r " )
t h a t , f o r t h e o n e ( 1 ) y e a r p e r i o d c o m m e n c i n g o n t h e d a t e t h e P r o d u c t w a s p u r c h a s e d ( t h e
" W a r r a n t y P e r i o d " ) , t h e P r o d u c t w i l l b e s u b s t a n t i a l l y f r e e f r o m d e f e c t s i n m a t e r i a l s a n d
w o r k m a n s h i p u n d e r n o r m a l u s e a n d c o n d i t i o n s . E l e c t r i c a l d a m a g e i s n o t a n i t e m t h a t i s
c o v e r e d u n d e r t h i s w a r r a n t y o r e x t e n d e d w a r r a n t i e s . O p t i o n a l t w o ( 2 ) y e a r a n d t h r e e ( 3 ) y e a r
w a r r a n t i e s a r e a v a i l a b l e t o e x t e n d t h i s c o v e r a g e i f p u r c h a s e d d u r i n g t h e f i r s t y e a r o f
c o v e r a g e .
I f a u t h o r i z e d b y E n a b l e -I T t o r e t u r n a P r o d u c t w h i c h d o e s n o t c o n f o r m t o t h e w a r r a n t y s e t
f o r t h a b o v e , t h e E n d U s e r m u s t : ( 1 ) o b t a i n a r e t u r n m a t e r i a l s a u t h o r i z a t i o n ( R M A ) n u m b e r
f r o m E n a b l e -I T b y c o n t a c t i n g t h e C u s t o m e r S e r v i c e D e p t . a t 8 8 8 -3 0 9 -0 9 1 0 b e t w e e n t h e
h o u r s o f 8 : 0 0 a . m . a n d 5 : 0 0 p . m . P S T a n d o t h e r w i s e f u l l y c o m p l y w i t h E n a b l e -I T ’ s t h e n c u r r e n t R M A p o l i c y ; ( 2 ) r e t u r n t h e P r o d u c t t o E n a b l e -I T , I n c . i n i t s o r i g i n a l p a c k a g i n g f r e i g h t
p r e -p a i d ; a n d ( 3 ) p r o v i d e t o E n a b l e -I T t h e o r i g i n a l r e c e i p t o r b i l l o f s a l e e s t a b l i s h i n g t h e d a t e
o n w h i c h t h e P r o d u c t w a s p u r c h a s e d .
Page 91
P a g e 9 1 o f
9 3
Please ship Authorized RMAs to:
Enable-IT Processing Facility
16600 Harbor Blvd, Ste G
Fountain Valley, CA 92708
Returning Products for Refund
30-Day refund applies to single kit Ethernet Extenders only and is subject to a 25%
Restocking Fee. Shipments without valid / authorized RMA number or sent to our
corporate Las Vegas Address can be refused and or billed for additional shipping.
Enable-IT Limited Warranty
E n a b l e -I T w a r r a n t s t h e Enable-IT 8424 WiFi AP Units s o l e l y p u r s u a n t t o t h e f o l l o w i n g t e r m s
a n d c o n d i t i o n s .
1 . P R O D U C T W A R R A N T Y
a . E x p r e s s W a r r a n t y E n a b l e -I T w a r r a n t s t o t h e o r i g i n a l p u r c h a s e r o f t h e P r o d u c t ( " y o u " o r t h e
" E n d U s e r " ) t h a t , f o r t h e o n e ( 1 ) y e a r p e r i o d c o m m e n c i n g o n t h e d a t e t h e P r o d u c t w a s
p u r c h a s e d ( t h e " W a r r a n t y P e r i o d " ) , t h e P r o d u c t w i l l b e s u b s t a n t i a l l y f r e e f r o m d e f e c t s i n
m a t e r i a l s a n d w o r k m a n s h i p u n d e r n o r m a l u s e a n d c o n d i t i o n s . T h i s w a r r a n t y d o e s n o t a p p l y
t o P r o d u c t s w h i c h a r e r e s o l d a s u s e d , r e p a i r e d o r r e c o n d i t i o n e d o r c o n s u m a b l e s ( s u c h a s
b a t t e r i e s ) s u p p l i e d w i t h t h e P r o d u c t . E n a b l e -I T d o e s n o t m a k e a n y w a r r a n t y w i t h r e s p e c t t o
a n y t h i r d p a r t y p r o d u c t , s o f t w a r e o r a c c e s s o r y s u p p l i e d w i t h o r u s e d i n c o n n e c t i o n w i t h t h e
P r o d u c t a n d s u c h t h i r d p a r t y p r o d u c t s , s o f t w a r e a n d a c c e s s o r i e s , i f a n y , a r e p r o v i d e d " A S I S . "
W a r r a n t y c l a i m s r e l a t e d t o s u c h t h i r d p a r t y p r o d u c t s , s o f t w a r e a n d a c c e s s o r i e s m u s t b e m a d e
t o t h e a p p l i c a b l e t h i r d p a r t y m a n u f a c t u r e r .
b . R e m e d i e s f o r B r e a c h o f W a r r a n t y I n t h e e v e n t o f a b r e a c h o f t h e f o r e g o i n g w a r r a n t y ,
E n a b l e -I T w i l l , i n i t s s o l e d i s c r e t i o n a n d a t i t s c o s t a n d s u b j e c t t o t h e t e r m s o f t h e f o l l o w i n g
p a r a g r a p h , r e p a i r t h e n o n -c o n f o r m i n g P r o d u c t , r e p l a c e t h e n o n -c o n f o r m i n g P r o d u c t w i t h a
n e w o r r e c o n d i t i o n e d P r o d u c t o r r e f u n d o f t h e p u r c h a s e p r i c e f o r t h e P r o d u c t . A n y n e w o r
r e c o n d i t i o n e d P r o d u c t p r o v i d e d p u r s u a n t t o t h i s p a r a g r a p h i s w a r r a n t e d a s p r o v i d e d h e r e i n
f o r t h e r e m a i n d e r o f t h e o r i g i n a l W a r r a n t y P e r i o d . T H E R E M E D Y S E T F O R T H I N T H I S
P A R A G R A P H S H A L L B E T H E E N D U S E R ’ S S O L E A N D E X C L U S I V E R E M E D Y F O R
B R E A C H O F T H E F O R E G O I N G W A R R A N T Y .
c . C o n d i t i o n s f o r W a r r a n t y Q u a l i f i c a t i o n I f a u t h o r i z e d b y E n a b l e -I T t o r e t u r n a P r o d u c t w h i c h
d o e s n o t c o n f o r m t o t h e w a r r a n t y s e t f o r t h a b o v e , t h e E n d U s e r m u s t : ( 1 ) o b t a i n a r e t u r n
m a t e r i a l s a u t h o r i z a t i o n ( R M A ) n u m b e r f r o m E n a b l e -I T b y c o n t a c t i n g t h e C u s t o m e r S e r v i c e
D e p t . a t 8 8 8 -3 0 9 -0 9 1 0 b e t w e e n t h e h o u r s o f 8 : 0 0 a . m . a n d 5 : 0 0 p . m . P S T a n d o t h e r w i s e f u l l y
c o m p l y w i t h E n a b l e -I T ’ t h e n -c u r r e n t R M A p o l i c y ; ( 2 ) r e t u r n t h e P r o d u c t t o E n a b l e -I T i n i t s
o r i g i n a l p a c k a g i n g f r e i g h t p r e -p a i d ; a n d ( 3 ) p r o v i d e t o En a b l e -I T t h e o r i g i n a l r e c e i p t o r b i l l o f
s a l e e s t a b l i s h i n g t h e d a t e o n w h i c h t h e P r o d u c t w a s p u r c h a s e d .
P r o d u c t s r e t u r n e d t o E n a b l e -I T w i t h o u t a n R M A n u m b e r w i l l b e r e t u r n e d t o t h e E n d U s e r .
E n a b l e -I T s h a l l n o t b e r e s p o n s i b l e f o r d a m a g e o r l o s s d u r i n g s h i p m e n t o f t h e r e t u r n e d
P r o d u c t t o E n a b l e -I T .
Page 92
P a g e 9 2 o f
9 3
d . V o i d i n g o f W a r r a n t y . T h e e x p r e s s w a r r a n t y s e t f o r t h a b o v e s h a l l n o t a p p l y t o f a i l u r e o f t h e
P r o d u c t i f t h e P r o d u c t h a s b e e n s u b j e c t e d t o : ( i ) p h y s i c a l a b u s e , m i s u s e , i m p r o p e r
i n s t a l l a t i o n , a b n o r m a l u s e , p o w e r f a i l u r e o r s u r g e , o r u s e n o t c o n s i s t e n t w i t h t h e o p e r a t i n g
i n s t r u c t i o n s p r o v i d e d b y E n a b l e -I T ; ( i i ) m o d i f i c a t i o n ( i n c l u d i n g b u t n o t l i m i t e d t o o p e n i n g t h e
P r o d u c t h o u s i n g ) o r r e p a i r b y a n y p a r t y i n a n y m a n n e r o t h e r t h a n a s a p p r o v e d b y E n a b l e -I T
in w r i t i n g ; ( i i i ) f r a u d , t a m p e r i n g , u n u s u a l p h y s i c a l o r e l e c t r i c a l s t r e s s , u n s u i t a b l e o p e r a t i n g o r
p h y s i c a l c o n d i t i o n s , n e g l i g e n c e o r a c c i d e n t s ; ( i v ) r e m o v a l o r a l t e r a t i o n o f t h e P r o d u c t s e r i a l
n u m b e r t a g ; ( v ) i m p r o p e r p a c k a g i n g o f P r o d u c t r e t u r n s ; o r ( v i ) d a m a g e d u r i n g s h i p m e n t ( o t h e r
t h a n d u r i n g t h e o r i g i n a l s h i p m e n t o f t h e P r o d u c t t o t h e E n d U s e r f r o m E n a b l e -I T , i f
a p p l i c a b l e ) .
e . W a r r a n t y D i s c l a i m e r s T H E E X P R E S S W A R R A N T Y S E T F O R T H A B O V E I S I N L I E U O F
A L L O T H E R W A R R A N T I E S , W H E T H E R W R I T T E N , O R A L , E X P R E S S O R I M P L I E D .
E N A B L E -I T D I S C L A I M S , T O T H E M A X I M U M E X T E N T P E R M I T T E D B Y L A W , T H E
I M P L I E D W A R R A N T I E S O F M E R C H A N T A B I L I T Y , F I T N E S S F O R A P A R T I C U L A R
P U R P O S E O R N O N I N F R I N G E M E N T O F T H I R D P A R T Y R I G H T S . N O P E R S O N
( I N C L U D I N G W I T H O U T L I M I T A T I O N , E N A B L E -I T ’ E M P L O Y E E S , A G E N T S , R E S E L L E R S ,
O E M S O R D I S T R I B U T O R S ) I S A U T H O R I Z E D T O M A K E A N Y O T H E R W A R R A N T Y O R
R E P R E S E N T A T I O N C O N C E R N I N G T H E P R O D U C T . I F T H E D I S C L A I M E R O F A N Y
I M P L I E D W A R R A N T Y I S N O T P E R M I T T E D B Y L A W , T H E D U R A T I O N O F A N Y S U C H
I M P L I E D W A R R A N T Y I S L I M I T E D T O O N E ( 1 ) Y E A R F R O M T H E D A T E O F P U R C H A S E .
S O M E J U R I S D I C T I O N S D O N O T A L L O W T H E E X C L U S I O N O F I M P L I E D W A R R A N T I E S
O R L I M I T A T I O N S O N H O W L O N G A N I M P L I E D W A R R A N T Y M A Y L A S T , S O S U C H
L I M I T A T I O N S O R E X C L U S I O N S M A Y N O T A P P L Y . T H I S W A R R A N T Y G I V E S T H E E N D
U S E R S P E C I F I C L E G A L R I G H T S A N D T H E E N D U S E R M A Y A L S O H A V E O T H E R
R I G H T S W H I C H V A R Y F R O M J U R I S D I C T I O N T O J U R I S D I C T I O N . E N A B L E -I T D O E S
N O T W A R R A N T T H A T T H E O P E R A T I O N O F T H E P R O D U C T W I L L B E
U N I N T E R R U P T E D O R E R R O R F R E E .
E N A B L E -I T I S N O T R E S P O N S I B L E F O R A N Y D A M A G E T O O R L O S S O F A N Y
P R O G R A M S , D A T A , O R O T H E R I N F O R M A T I O N S T O R E D O N O R T R A N S M I T T E D
U S I N G T H E P R O D U C T .
2 . L I M I T A T I O N O F L I A B I L I T Y I N N O E V E N T S H A L L E N A B L E -I T B E L I A B L E T O T H E E N D
U S E R O R A N Y T H I R D P A R T Y F O R A N Y I N D I R E C T , S P E C I A L , P U N I T I V E , I N C I D E N T A L
O R C O N S E Q U E N T I A L D A M A G E S I N C O N N E C T I O N W I T H O R A R I S I N G O U T O F T H E
S A L E O R U S E O F T H E P R O D U C T ( I N C L U D I N G B U T N O T L I M I T E D T O L O S S O F
P R O F I T , U S E , D A T A , O R O T H E R E C O N O M I C A D V A N T A G E ) , H O W E V E R I T A R I S E S ,
I N C L U D I N G W I T H O U T L I M I T A T I O N B R E A C H O F W A R R A N T Y , O R I N C O N T R A C T O R I N
T O R T ( I N C L U D I N G N E G L I G E N C E ) , O R S T R I C T L I A B I L I T Y , E V E N I F E N A B L E -I T H A S
B E E N P R E V I O U S L Y A D V I S E D O F T H E P O S S I B I L I T Y O F S U C H D A M A G E A N D E V E N I F
A L I M I T E D R E M E D Y S E T F O R T H I N T H I S A G R E E M E N T F A I L S O F I T S E S S E N T I A L
P U R P O S E . I N N O E V E N T S H A L L E N A B L E -I T ’ L I A B I L I T Y T O T H E E N D U S E R O R A N Y
T H I R D P A R T Y E X C E E D T H E P R I C E P A I D F O R T H E P R O D U C T . B E C A U S E S O M E
J U R I S D I C T I O N S D O N O T A L L O W T H E E X C L U S I O N O R L I M I T A T I O N O F L I A B I L I T Y F O R
C O N S E Q U E N T I A L O R I N C I D E N T A L D A M A G E S , T H E A B O V E L I M I T A T I O N S M A Y
N O T A P P L Y T O T H E E N D U S E R .
3 . L I C E N S E A N D L I M I T A T I O N S . T h e f i r m w a r e a n d s o f t w a r e e m b e d d e d i n t h e P r o d u c t ( t h e
" E m b e d d e d S o f t w a r e " ) a r e l i c e n s e d t o y o u . Y o u r u s e o f t h e P r o d u c t i s y o u r a c c e p t a n c e o f t h e
w a r r a n t y t e r m s a b o v e a n d t h e t e r m s b e l o w . Y o u m a y u s e t h e E m b e d d e d S o f t w a r e s o l e l y i n
Page 93
P a g e 9 3 o f
9 3
c o n j u n c t i o n w i t h y o u r u s e o f t h e P r o d u c t . A l l w o r l d w i d e r i g h t , t i t l e a n d i n t e r e s t i n a n d t o t h e
P r o d u c t , o r a n y p o r t i o n t h e r e o f ( i n c l u d i n g b u t n o t l i m i t e d t o t h e E m b e d d e d S o f t w a r e ) ,
i n c l u d i n g a l l c o p y r i g h t s , p a t e n t r i g h t s , t r a d e m a r k s , t r a d e s e c r e t s , a n d o t h e r i n t e l l e c t u a l
p r o p e r t y r i g h t s t h e r e i n a n d t h e r e t o , a r e a n d s h a l l r e m a i n t h e e x c l u s i v e p r o p e r t y o f E n a b l e -I T
a n d / o r i t s l i c e n s o r s . Y o u a c k n o w l e d g e a n d a g r e e t h a t y o u m a y n o t , a n d m a y n o t a l l o w a n y
t h i r d p a r t y t o , ( i ) u s e t h e E m b e d d e d S o f t w a r e i n a m a n n e r t h a t i s i n c o n s i s t e n t w i t h t h e a b o v e
e x p r e s s r i g h t g r a n t e d t o y o u o r ( i i ) m o d i f y , d i s t r i b u t e , r e p r o d u c e , d e c o m p i l e , d i s a s s e m b l e ,
r e v e r s e e n g i n e e r o r o t h e r w i s e a t t e m p t t o d i s c o v e r t h e s o u r c e c o d e f o r t h e E m b e d d e d
S o f t w a r e .
Contact Us
European Sales: North American Sales: Asia Pacific Sales:
+1 714 362-0689 +1 888 309-0910 +61 02 8898-9622
+1 320 215-6907 fax +1 866 389-8605 fax +61 2 9939-0005 fax
http://www.enable-it.eu http://www.enableit.com http://www.enable-it.com.au
[email protected] [email protected] [email protected]
 Loading...