

Page 1

SonicWall TZ series
Exceptional security and stellar performance at a disruptively low TCO
The SonicWall TZ series of Unied Threat
Management (UTM) rewalls is ideally
suited for any organization that requires
enterprise-grade network protection.
SonicWall TZ series rewalls provide
broad protection with advanced
security services consisting of onbox and cloud-based anti-malware,
anti-spyware, application control,
intrusion prevention system (IPS), and
URL ltering. To counter the trend of
encrypted attacks, the TZ series has the
processing power to inspect encrypted
SSL/TLS connections against the latest
threats. Combined with Dell X-Series
switches, selected TZ series rewalls can
directly manage the security of these
additional ports.
Backed by the SonicWall Capture
Threat Network, the SonicWall TZ
series delivers continuous updates to
maintain a strong network defense
against cybercriminals. The SonicWall
TZ series is able to scan every byte of
every packet on all ports and protocols
with almost zero latency and no le
size limitations.
The SonicWall TZ series features Gigabit
Ethernet ports, optional integrated
802.11ac wireless*, IPSec and SSL VPN,
failover through integrated 3G/4G
support, load balancing and network
segmentation. The SonicWall TZ series
UTM rewalls also provide fast, secure
mobile access over Apple iOS, Google
Android, Amazon Kindle, Windows,
Mac OS X and Linux platforms.
The SonicWall Global Management
System (GMS) enables centralized
deployment and management of
SonicWall TZ series rewalls from a
single system.
Managed security for
distributed environments
Schools, retail shops, remote sites,
branch ofces and distributed
enterprises need a solution that
integrates with their corporate
rewall. SonicWall TZ series rewalls
share the same code base—and
same protection—as our agship
SuperMassive next-generation rewalls.
This simplies remote site management,
as every administrator sees the same
user interface (UI). GMS enables
network administrators to congure,
monitor and manage remote SonicWall
rewalls through a single pane of
glass. By adding high-speed, secure
wireless, the SonicWall TZ series extends
the protection perimeter to include
customers and guests frequenting the
retail site or remote ofce.
Benets:
• Enterprise grade network
protection
• Deep packet inspection of all trafc
without restrictions on le size or
protocol
• Secure 802.11ac wireless
connectivity using integrated
wireless controller or via
external SonicPoint wireless access
points
• SSL VPN mobile access for Apple
iOS, Google Android, Amazon
Kindle, Windows, Mac OS and
Linux devices
• Over 100 additional por ts can
be securely managed by the
TZ console when deployed in
combination with Dell X-Series
switches
* 802.11ac currently not available on SOHO models; SOHO models support 802.11a/b/g/n
Page 2

SonicWall TZ600 series
For emerging enterprises, retail and branch ofces looking for security performance at a value price, the SonicWall TZ600 nextgeneration rewall secures networks with enterprise-class features and uncompromising performance.
Specication TZ600 series
Firewall throughput 1.5 Gbps
Full DPI throughput 500 Mbps
Anti-malware throughput 500 Mbps
IPS throughput 1.1 Gbps
IMIX throughput 900 Mbps
Max DPI connections 125,000
New connections/sec 12,000
Power LED Test LED
USB port
(3G/4G WAN
failover)
Link and
activity
indicator LEDs
Expansion
module
Console
port
8x1-GbE
switch
(congurable)
X0 LAN port
X1 WAN port
SonicWall TZ500 series
For growing branch ofces and SMBs, the SonicWall TZ500 series delivers highly effective, no-compromise protection with
network productivity and optional integrated 802.11ac dual-band wireless.
Specication TZ500 series
Firewall throughput 1.4 Gbps
Full DPI throughput 400 Mbps
Anti-malware throughput 400 Mbps
IPS throughput 1.0 Gbps
IMIX throughput 700 Mbps
Max DPI connections 100,000
New connections/sec 8,000
Optional
802 .11ac
wireless
Secure
power
Power LED Test LED 6x1-GbE
USB port
(3G/4G WAN
failover)
Link and
activity
indicator LEDs
Console
port
switch
(congurable)
X0 LAN port
X1 WAN port
Secure
power
2
Page 3

SonicWall TZ400 series
For small business, retail and branch ofce locations, the SonicWall TZ400 series delivers enterprise-grade protection. Flexible
wireless deployment is available with optional 802.11ac dual-band wireless integrated into the rewall.
Specication TZ400 series
Firewall throughput 1.3 Gbps
Full DPI throughput 300 Mbps
Anti-malware throughput 300 Mbps
IPS throughput 900 Mbps
IMIX throughput 500 Mbps
Max DPI connections 90,000
New connections/sec 6,000
Optional
802 .11ac
wireless
Power LED Test LED 5x1-GbE switch
USB port
(3G/4G WAN
failover)
Link and
activity
indicator
Console
port
(congurable)
X0 LAN port
X1 WAN port
Secure
power
LEDs
SonicWall TZ300 series
The SonicWall TZ300 series offers an all-in-one solution that protects networks from attack. Unlike consumer grade products, the
SonicWall TZ300 series rewall combines effective intrusion prevention, anti-malware and content/URL ltering with optional
802.11ac integrated wireless and broadest secure mobile platforms support for laptops, smartphones and tablets.
Specication TZ300 series
Firewall throughput 750 Mbps
Full DPI throughput 100 Mbps
Anti-malware throughput 100 Mbps
IPS throughput 300 Mbps
IMIX throughput 200 Mbps
Max DPI connections 50,000
New connections/sec 5,000
Optional
802 .11ac
wireless
Power LED Test LED
USB port
(3G/4G WAN
failover)
Link and
activity
indicator LEDs
Console
port
3x1-GbE switch
(congurable)
X0 LAN port
X1 WAN port
Secure
power
3
Page 4

SonicWall SOHO series
For wired and wireless small and home ofce environments, the SonicWall SOHO series delivers the same business-class protection
large organizations require at a more affordable price point.
Specication SOHO series
Firewall throughput 300 Mbps
Full DPI throughput 50 Mbps
Anti-malware throughput 50 Mbps
IPS throughput 100 Mbps
IMIX throughput 60 Mbps
Max DPI connections 10,000
New connections/sec 1,8 00
Optional
802 .11n
wireless
Power LED Test LED
Link and
activity
indicator LEDs
USB port
(3G/4G WAN
failover)
Extensible architecture for extreme scalability
and performance
The Reassembly-Free Deep Packet Inspection (RFDPI) engine
is designed from the ground up with an emphasis on providing
security scanning at a high performance level, to match both
the inherently parallel and ever-growing nature of network
trafc. When combined with multi-core processor systems, this
parallel-centric software architecture scales up perfectly to
NSA or SuperMassive
Corporate
Headquarters
Console
port
3x1-GbE switch
(congurable)
X0 LAN port
X1 WAN port
Secure
power
address the demands of deep packet inspection at high trafc
loads. The SonicWall TZ Series platform relies on processors
that, unlike x86, are optimized for packet, crypto and network
processing while retaining exibility and programmability in
the eld — a weak point for ASICs systems. This exibility is
essential when new code and behavior updates are necessary
to protect against new attacks that require updated and more
sophisticated detection techniques.
SOHO
Home office
Internet
TZ400
Global Management System
TZ600
18 port
X-Series switch
Small
branch office
Large
branch office
4
Page 5

Reassembly-Free Deep Packet Inspection
(RFDPI) engine
The RFDPI engine provides superior threat protection and
application control without compromising performance. This
patented engine inspects the trafc stream to detect threats
at Layers 3-7. The RFDPI engine takes network streams through
extensive and repeated normalization and decryption in
order to neutralize advanced evasion techniques that seek
to confuse detection engines and sneak malicious code
into the network. Once a packet undergoes the necessary
preprocessing, including SSL decryption, it is analyzed against
a single proprietary memory representation of three signature
databases: intrusion attacks, malware and applications. The
connection state is then advanced to represent the position
of the stream relative to these databases until it encounters
a state of attack, or another “match” event, at which point a
pre-set action is taken. As malware is identied, the SonicWall
rewall terminates the connection before any compromise
can be achieved and properly logs the event. However, the
engine can also be congured for inspection only or, in the
case of application detection, to provide Layer 7 bandwidth
management services for the remainder of the application
stream as soon as the application is identied.
Packet assembly-based process
Packet
disassembly
Traffic out
Inspection capacity
Min Max
Traffic in
Inspection time
Less More
Proxy
Scanning
When proxy
becomes full or
content too large,
files bypass
scanning.
Global management and reporting
For larger, distributed enterprise deployments, the optional
SonicWall Global Management System (GMS) provides
administrators a unied, secure and extensible platform to
manage SonicWall security appliances and Dell X-Series
switches. It enables enterprises to easily consolidate the
management of security appliances, reduce administrative
and troubleshooting complexities and governs all operational
Packet reassembly-free process
Traffic in
Inspection time
Less More
Reassembly-free packet
scanning eliminates proxy
and content size limitations.
Traffic out
Inspection capacity
Min Max
SonicWall stream-based architectureCompetitive proxy-based architecture
aspects of the security infrastructure including centralized
policy management and enforcement, real-time event
monitoring, analytics and reporting, and more. GMS also meets
the rewall change management requirements of enterprises
through a workow automation feature. GMS provides a
better way to manage network security by business processes
and service levels that dramatically simplify the lifecycle
management of your overall security environments rather than
on a device-by-device basis.
5
Page 6
Security and protection
The dedicated, in-house SonicWall
Capture Labs threat research team
works on researching and developing
countermeasures to deploy to the
rewalls in the eld for up-to-date
protection. The team leverages more
than one million sensors across the
globe for malware samples, and for
telemetry feedback on the latest threat
information, which in turn is fed into
the intrusion prevention, anti-malware
and application detection capabilities.
SonicWall rewall customers with current
subscriptions are provided continuously
updated threat protection around
the clock, with new updates taking
effect immediately without reboots
or interruptions. The signatures on
the appliances protect against wide
classes of attacks, covering up to tens
of thousands of individual threats with
a single signature. In addition to the
countermeasures on the appliance, all
SonicWall rewalls also have access to
SonicWall CloudAV, which extends the
onboard signature intelligence with
more than 20 million signatures, and
growing. This CloudAV database is
accessed via a proprietary light-weight
protocol by the rewall to augment the
inspection done on the appliance. With
Geo-IP and botnet ltering capabilities,
SonicWall next-generation rewalls are
able to block trafc from dangerous
domains or entire geographies in order
to reduce the risk prole of the network.
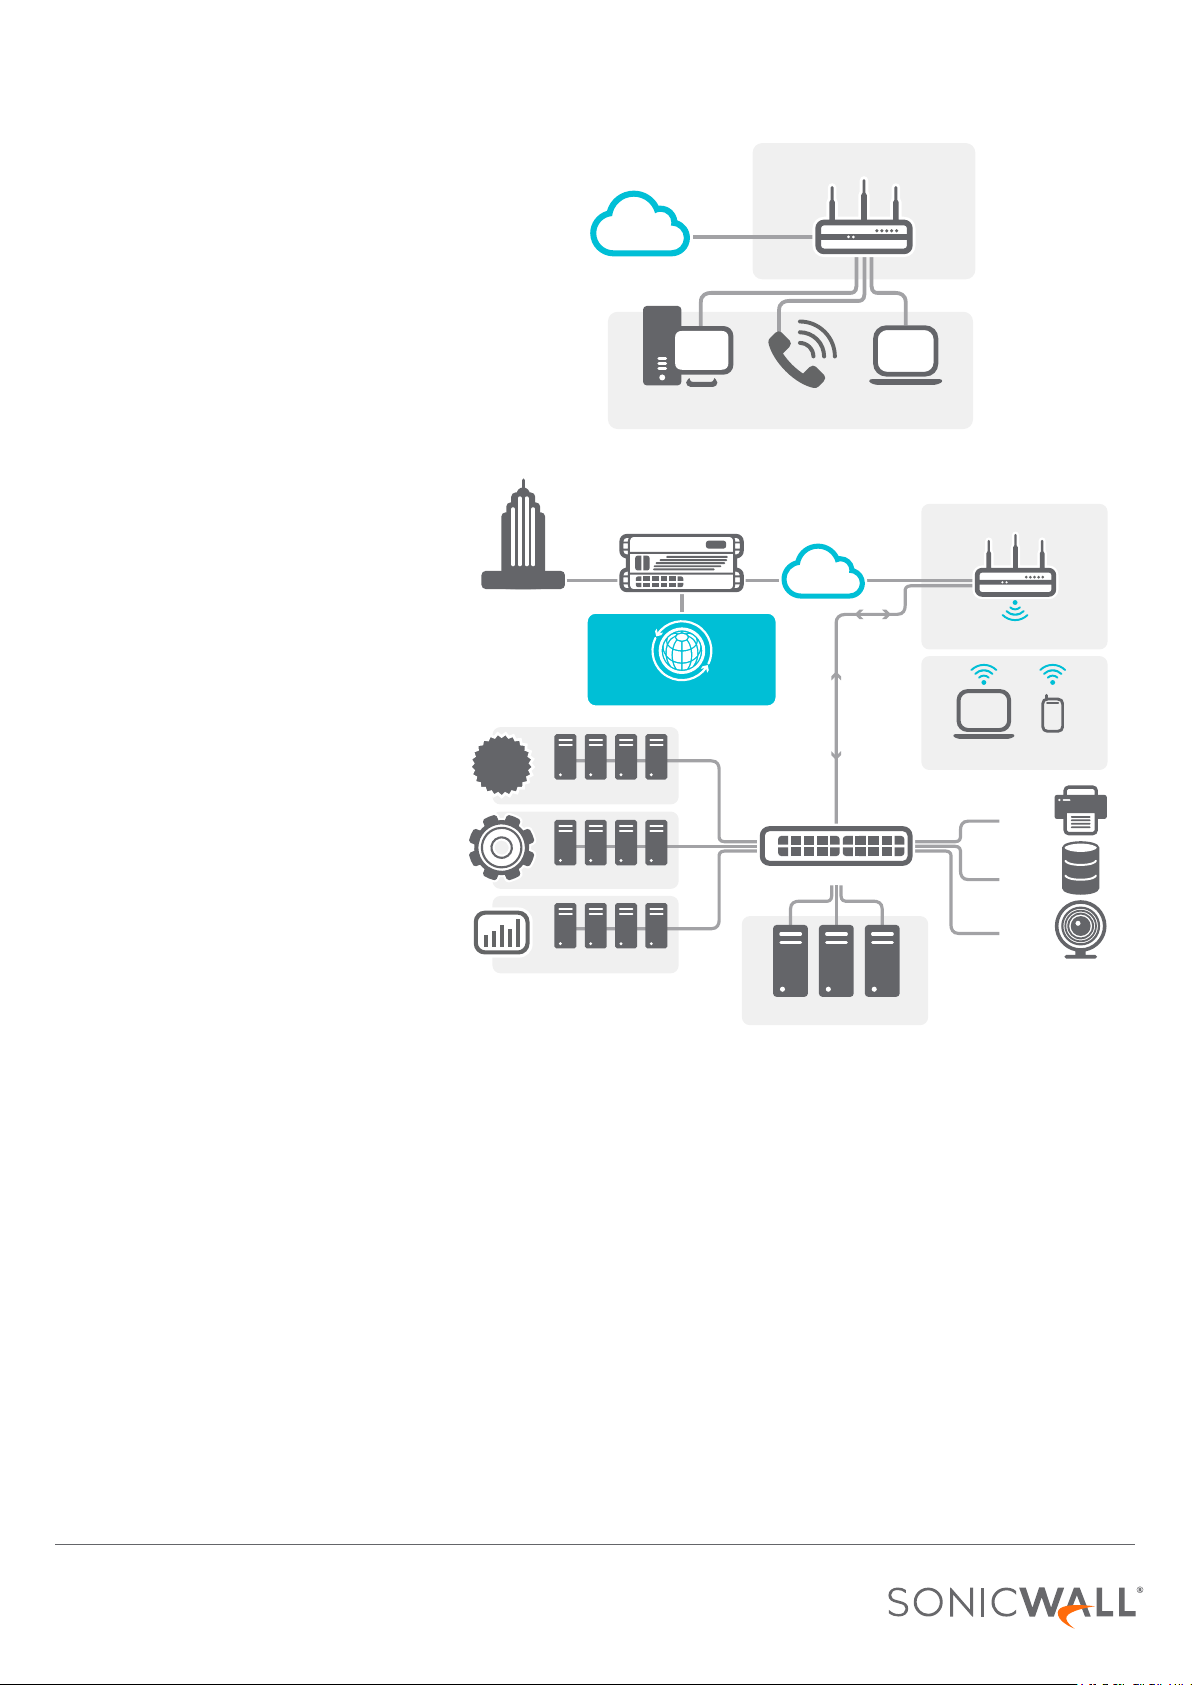
Corporate
Headquarters
$
Engineering network
Finance network
Internet
NSA or SuperMassive
Global Management System
Sales network
TZ product line
Home office / small office LAN
Internet
18-port X-Series switch
Protected server network
TZ product line
3G/analog failover
Secure wireless zone
Printers
Storage
PoE
cameras
Application intelligence
and control
granular insight into application
trafc, bandwidth utilization and
security threats, as well as powerful
Application intelligence informs
administrators of application trafc
traversing the network, so they can
schedule application controls based on
business priority, throttle unproductive
applications and block potentially
dangerous applications. Real-time
visualization identies trafc anomalies
troubleshooting and forensics
capabilities. Additionally, secure single
sign-on (SSO) capabilities enhance the
user experience, increase productivity
and reduce support calls. Management
of application intelligence and control
is simplied by using an intuitive webbased interface.
as they happen, enabling immediate
countermeasures against potential
inbound or outbound attacks or
performance bottlenecks. SonicWall
application trafc analytics provide
* 802.11ac currently not available on SOHO models; SOHO models support 802.11a/b/g/n
Flexible and secure wireless
Available as an optional feature, highspeed 802.11ac wireless* combines
with SonicWall next-generation
6
rewall technology to create a wireless
network security solution that delivers
comprehensive protection for wired and
wireless networks.
This enterprise-level wireless
performance enables WiFi-ready devices
to connect from greater distances
and use bandwidth-intensive mobile
apps, such as video and voice, in
higher density environments without
experiencing signal degradation.
Page 7
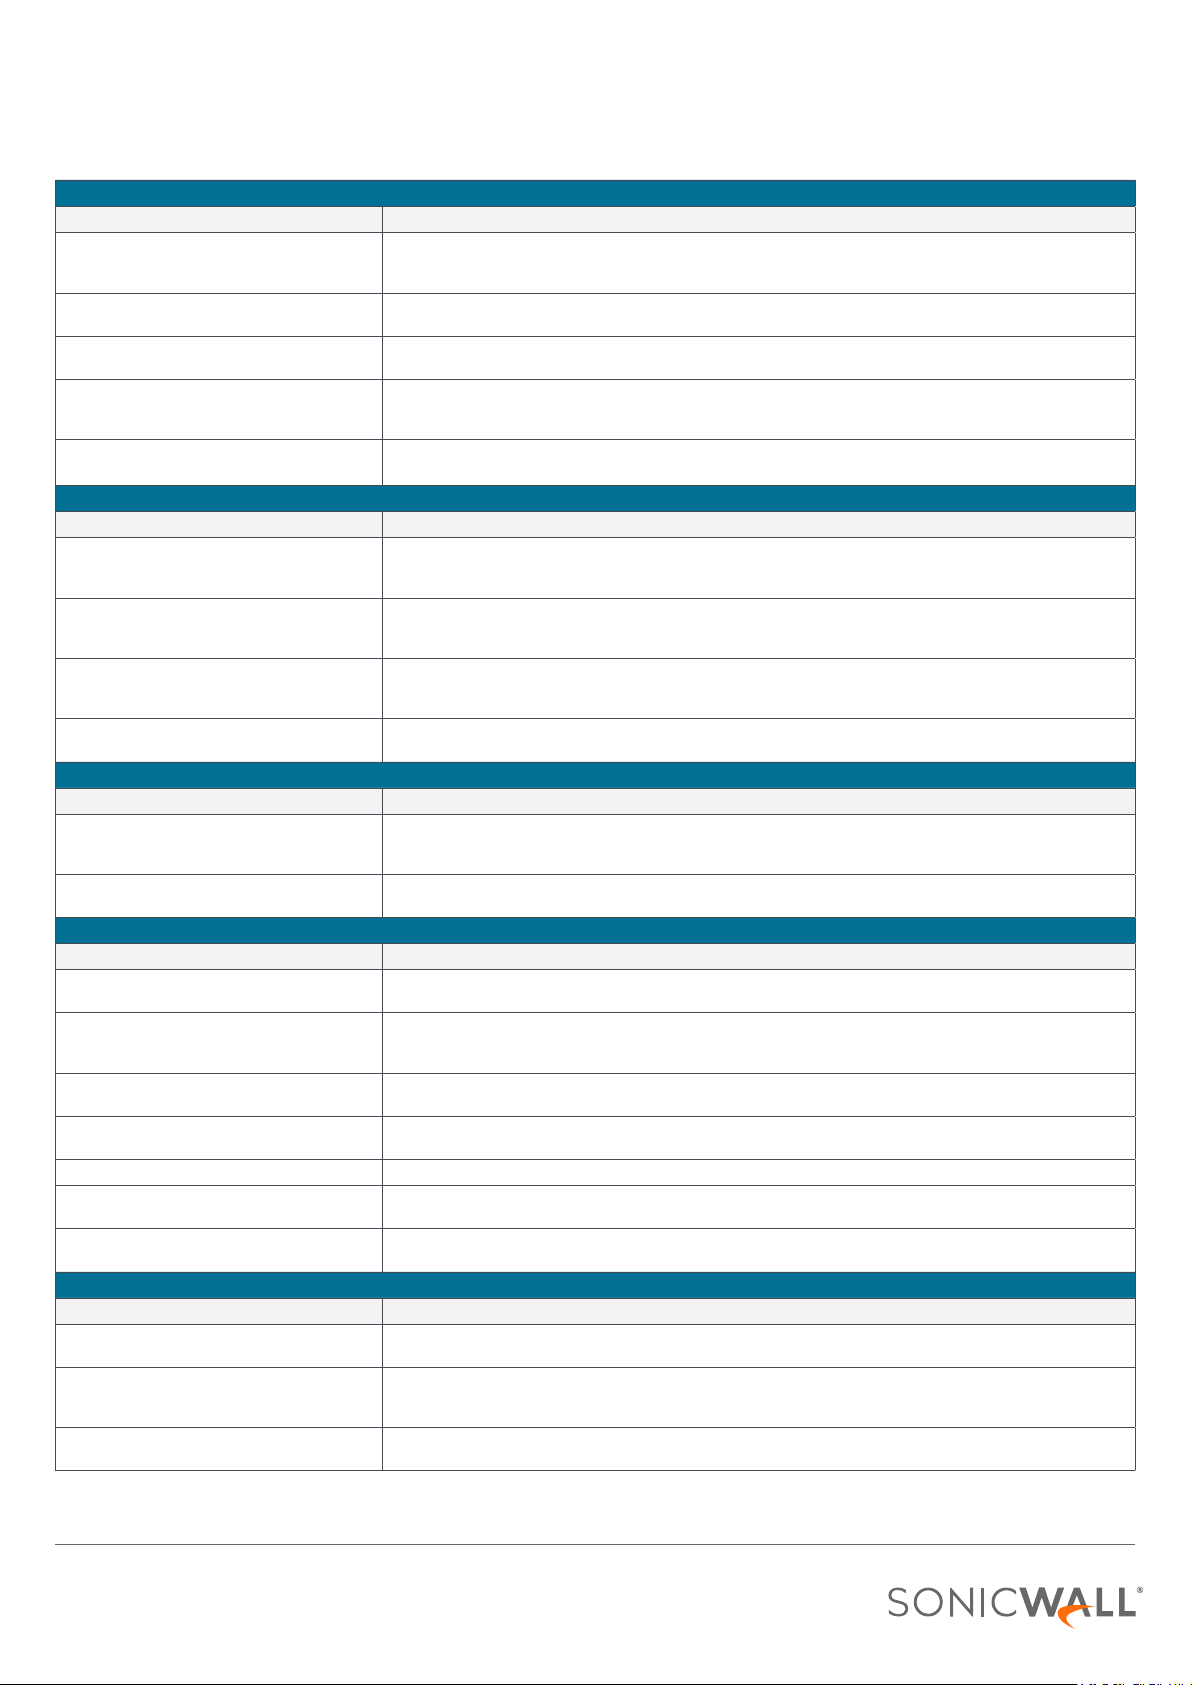
Features
RFDPI engine
Feature Description
Reassembly-Free Deep Packet Inspection This high-performance, proprietary and patented inspection engine performs stream based bi-directional trafc
Bi-directional inspection Scans for threats in both inbound and outbound trafc simultaneously to ensure that the network is not used to
Single-pass inspection A single-pass DPI architecture simultaneously scans for malware, intrusions and application identication, drastically
Stream-based inspection Proxy-less and non-buffering inspection technology provides ultra-low latency performance for deep packet
Deep Packet Inspection of Secure Socket Shell
(DPI-SSH)
Capture Advanced Threat Protection
Feature Description
Multi-engine sandboxing The multi-engine sandbox platform, which includes virtualized sandboxing, full system emulation, and hypervisor
Broad le type analysis Supports analysis of a broad range of le types, including executable programs (PE), DLL, PDFs, MS Ofce
Rapid deployment of signatures When a le is identied as malicious, a signature is immediately deployed to rewalls with SonicWall Capture
Block until verdict To prevent potentially malicious les from entering the network, les sent to the cloud for analysis can be held at the
Encrypted threat prevention
Feature Description
TLS/SSL decryption and inspection
SSH inspection
Intrusion prevention
Feature Description
Countermeasure-based protection Tightly integrated intrusion prevention system (IPS) leverages signatures and other countermeasures to scan packet
Automatic signature updates The SonicWall Capture Labs threat research team continuously researches and deploys updates to an extensive list of
Intra-zone IPS protection Bolsters internal security by segmenting the network into multiple security zones with intrusion prevention, preventing
Botnet command and control (CnC) detection
and blocking
Protocol abuse/anomaly Identies and blocks attacks that abuse protocols in an attempt to sneak past the IPS.
Zero-day protection Protects the network against zero-day attacks with constant updates against the latest exploit methods and
Anti-evasion technology Extensive stream normalization, decoding and other techniques ensure that threats do not enter the network
Threat prevention
Feature Description
Gateway anti-malware The RFDPI engine scans all inbound, outbound and intra-zone trafc for viruses, Trojans, key loggers and other
CloudAV malware protection A continuously updated database of over 20 million threat signatures resides in the SonicWall cloud servers and is
Around-the-clock security updates New threat updates are automatically pushed to rewalls in the eld with active security services, and take effect
analysis, without proxying or buffering, to uncover intrusion attempts, malware and identify application trafc
regardless of port.
distribute malware, and does not become a launch platform for attacks in case an infected machine is brought inside.
reducing DPI latency and ensuring that all threat information is correlated in a single architecture.
inspection of simultaneous network streams without introducing le and stream size limitations, and can be applied
on common protocols as well as raw TCP streams.
Detects and prevents advanced encrypted attacks that leverage SSH, blocks encrypted malware downloads, ceases
the spread of infections, and thwarts command and control communications and data exltration.
level analysis technology, executes suspicious code and analyzes behavior, providing comprehensive visibility to
malicious activity.
documents, archives, JAR, and APK plus multiple operating systems including Windows, Android, Mac OSX and
multi-browser environments.
subscriptions and Gateway Anti-Virus and IPS signature databases and the URL, IP and domain reputation databases
within 48 hours.
gateway until a verdict is determined.
Decrypts and inspects SSL trafc on the y, without proxying, for malware, intrusions and data leakage, and applies
application, URL and content control policies in order to protect against threats hidden in TLS/SSL encrypted trafc.
Included with security subscriptions for all models except SOHO. Sold as a separate license on SOHO.
Deep packet inspection of SSH (DPI-SSH) decrypts and inspects data traversing over SSH tunnels to prevent attacks
that leverage SSH.
payloads for vulnerabilities and exploits, covering a broad spectrum of attacks and vulnerabilities.
IPS countermeasures that covers more than 50 attack categories. The new updates take immediate effect without any
reboot or service interruption required.
threats from propagating across the zone boundaries.
Identies and blocks command and control trafc originating from bots on the local network to IPs and domains that
are identied as propagating malware or are known CnC points.
techniques that cover thousands of individual exploits.
undetected by utilizing evasion techniques in Layers 2-7.
malware in les of unlimited length and size across all ports and TCP streams.
referenced to augment the capabilities of the onboard signature database, providing RFDPI with extensive coverage
of threats.
immediately without reboots or interruptions.
7
Page 8
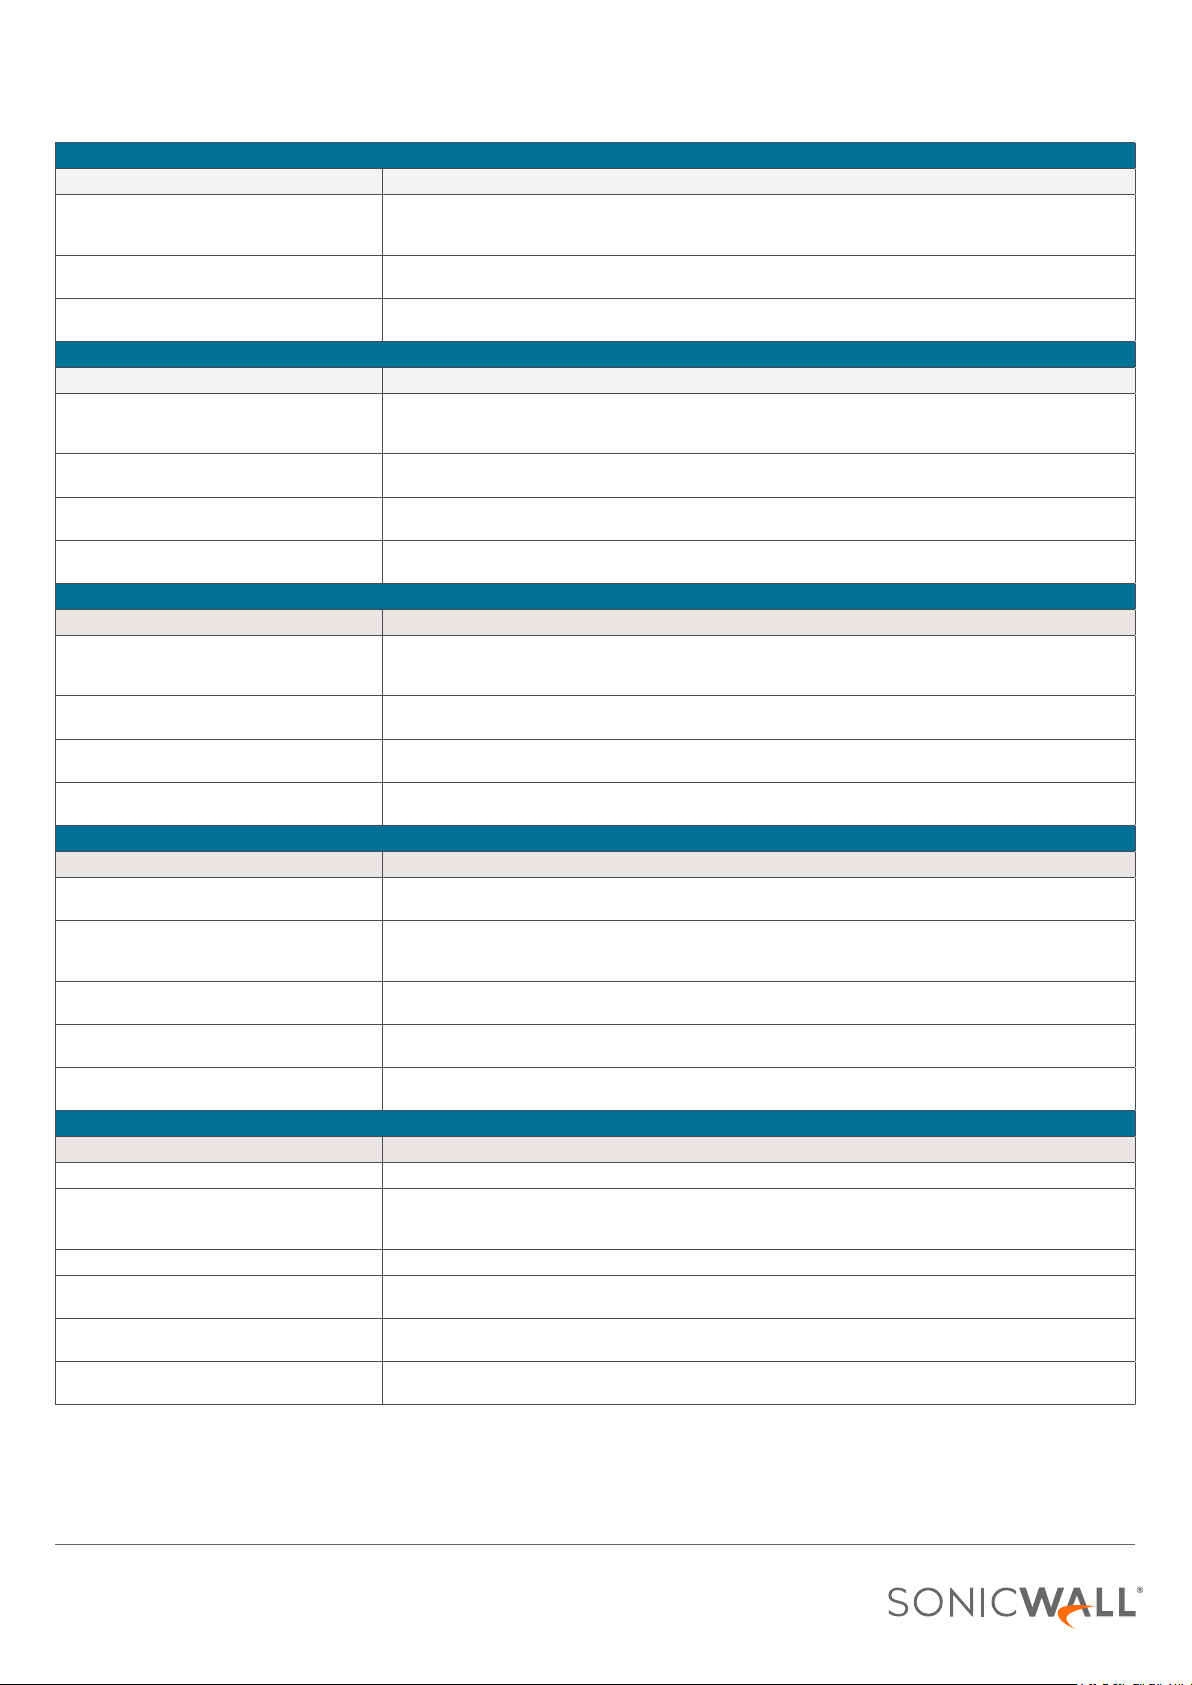
Threat prevention con't
Feature Description
SSL decryption and inspection Decrypts and inspects SSL trafc on the y, without proxying, for malware, intrusions and data leakage, and applies
Bi-directional raw TCP inspection The RFDPI engine is capable of scanning raw TCP streams on any port bi-directionally preventing attacks that they to
Extensive protocol support Identies common protocols such as HTTP/S, FTP, SMTP, SMBv1/v2 and others, which do not send data in raw TCP,
Application intelligence and control
Feature Description
Application control Control applications, or individual application features, that are identied by the RFDPI engine against a continuously
Custom application identication Control custom applications by creating signatures based on specic parameters or patterns unique to an application
Application bandwidth management Granularly allocate and regulate available bandwidth for critical applications or application categories while inhibiting
Granular control Control applications, or specic components of an application, based on schedules, user groups, exclusion lists and a
Content ltering
Feature Description
Inside/outside content ltering Enforce acceptable use policies and block access to websites containing information or images that are objectionable
Granular controls Block content using the predened categories or any combination of categories. Filtering can be scheduled by time
YouTube for Schools Enable teachers to choose from hundreds of thousands of free educational videos from YouTube EDU that are
Web caching URL ratings are cached locally on the SonicWall rewall so that the response time for subsequent access to frequently
Enforced anti-virus and anti-spyware
Feature Description
Multi-layered protection Utilize the rewall capabilities as the rst layer of defense at the perimeter, coupled with endpoint protection to
Automated enforcement option Ensure every computer accessing the network has the most recent version of anti-virus and anti-spyware signatures
Automated deployment and installation option Machine-by-machine deployment and installation of anti-virus and anti-spyware clients is automatic across the
Always on, automatic virus protection Frequent anti-virus and anti-spyware updates are delivered transparently to all desktops and le servers to improve
Spyware protection
Firewall and networking
Feature Description
Stateful packet inspection All network trafc is inspected, analyzed and brought into compliance with rewall access policies.
DDoS/DoS attack protection SYN Flood protection provides a defense against DOS attacks using both Layer 3 SYN proxy and Layer 2 SYN
Flexible deployment options
IPv6 support Internet Protocol version 6 (IPv6) is in its early stages to replace IPv4. With the latest SonicOS, the hardware will
Biometric authentication for remote access Supports mobile device authentication such as ngerprint recognition that cannot be easily duplicated or shared to
Dell X-Series switch integration Manage security settings of additional ports, including POE and POE+, under a single pane of glass using TZ series
application, URL and content control policies in order to protect against threats hidden in SSL encrypted trafc
Included with security subscriptions for all models except SOHO. Sold as a separate license on SOHO.
sneak by outdated security systems that focus on securing a few well-known ports.
and decodes payloads for malware inspection, even if they do not run on standard, well-known ports.
expanding database of over 3,500 application signatures, to increase network security and enhance network
productivity.
in its network communications, in order to gain further control over the network.
nonessential application trafc.
range of actions with full SSO user identication through LDAP/AD/Terminal Services/Citrix integration.
or unproductive with Content Filtering Service. Extend policy enforcement to block internet content for devices
located outside the rewall perimeter with the Content Filtering Client.
of day, such as during school or business hours, and applied to individual users or groups.
organized by subject and grade and align with common educational standards.
visited sites is only a fraction of a second.
block, viruses entering network through laptops, thumb drives and other unprotected systems.
installed and active, eliminating the costs commonly associated with desktop anti-virus and anti-spyware
management.
network, minimizing administrative overhead.
end user productivity and decrease security management.
Powerful spyware protection scans and blocks the installation of a comprehensive array of spyware programs on
desktops and laptops before they transmit condential data, providing greater desktop security and performance.
blacklisting technologies. Additionally, it provides the ability to protect against DOS/DDoS through UDP/ICMP ood
protection and connection rate limiting.
The SonicWall TZ Series can be deployed in traditional NAT, Layer 2 Bridge, Wire Mode and Network Tap modes.
support ltering implementations.
securely authenticate the user's identity for network access.
dashboard with X-Series switch (not available with the SOHO model)
8
Page 9
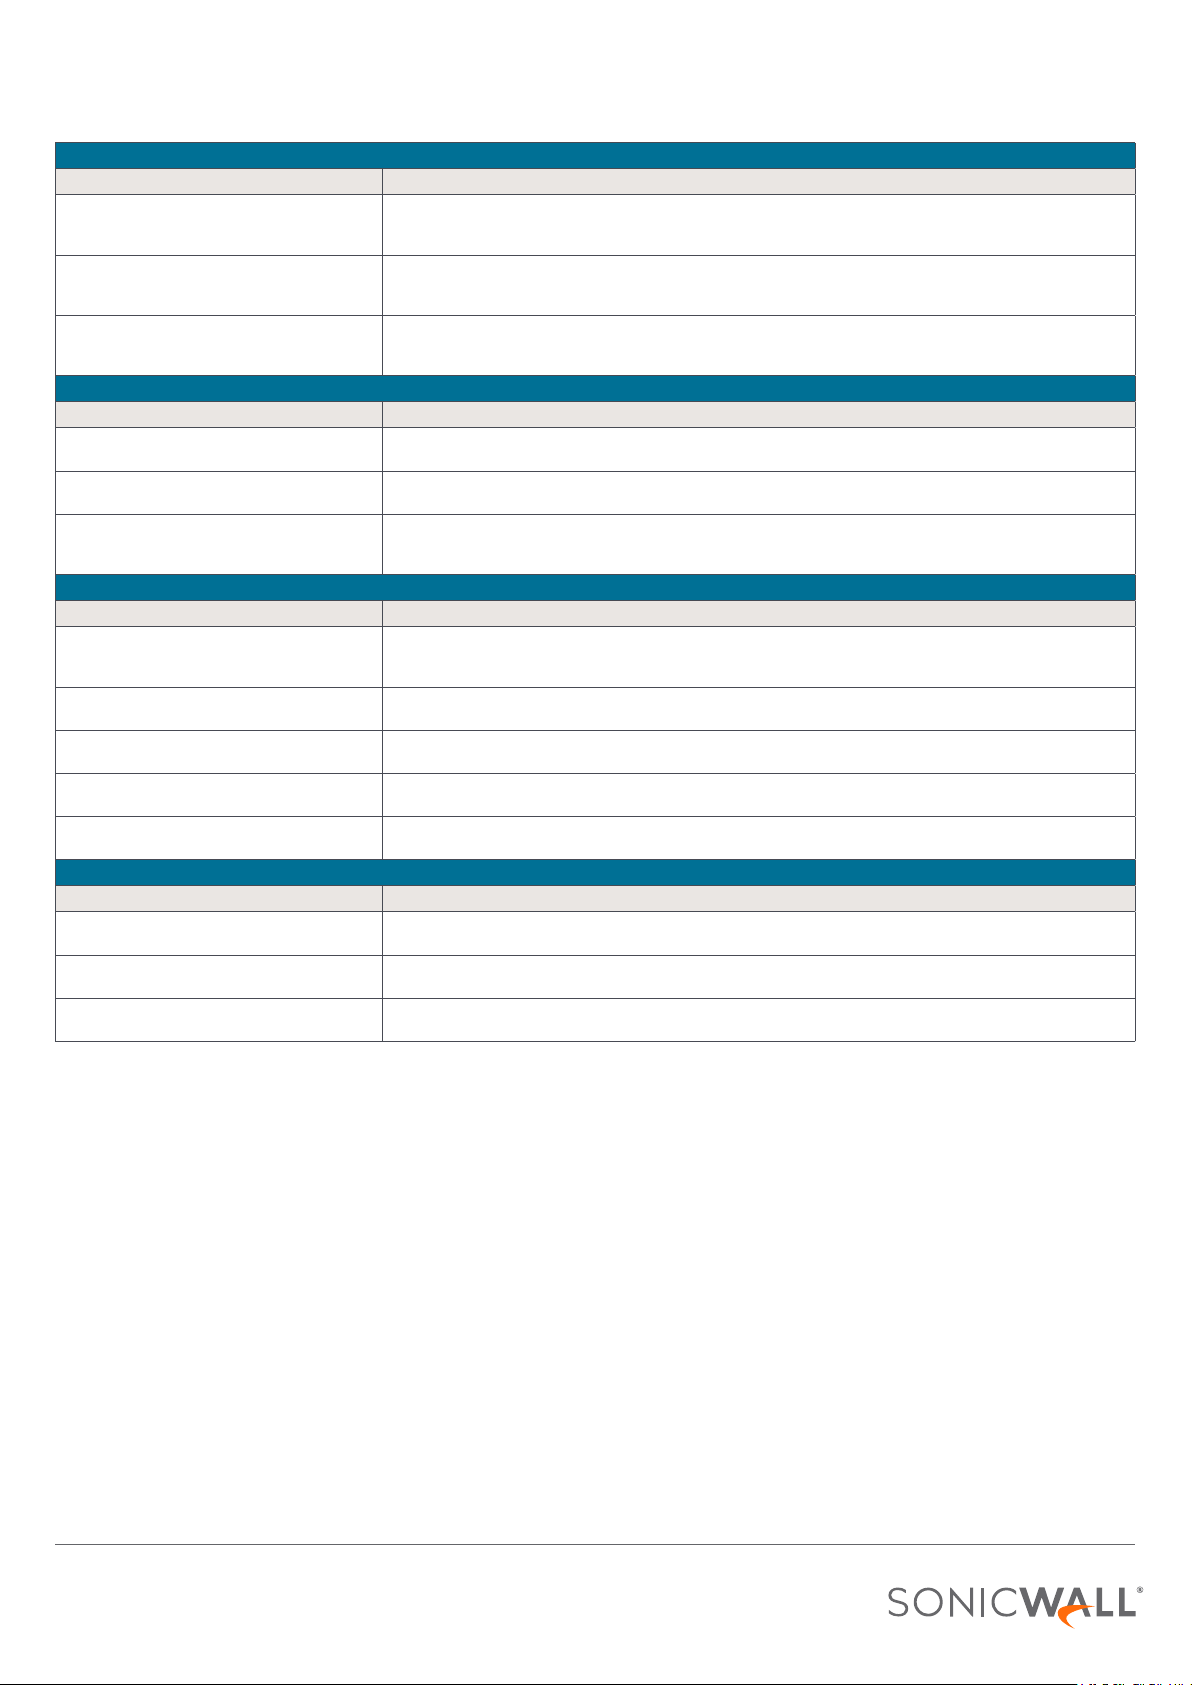
Firewall and networking con't
Feature Description
High availability SonicWall TZ500 and SonicWall TZ600 models support high availability with Active/Standby with
Threat API Enables the rewall to receive any and all proprietary, original equipment manufacturer and third-party intelligence
Wireless Network Security IEEE 802.11ac wireless technology can deliver up to 1.3 Gbps of wireless throughput with greater range and
Management and reporting
Feature Description
Global Management System SonicWall GMS monitors, congures and reports on multiple SonicWall appliances and Dell X-Series switches through
Powerful, single device management An intuitive, web-based interface allows quick and convenient conguration. Also, a comprehensive command line
IPFIX/NetFlow application ow reporting Exports application trafc analytics and usage data through IPFIX or NetFlow protocols for real-time and historical
Virtual Private Networking
Feature Description
Auto-provision VPN Simplies and reduces complex distributed rewall deployment down to a trivial effort by automating the initial
IPSec VPN for site-to-site connectivity High-performance IPSec VPN allows the SonicWall TZ Series to act as a VPN concentrator for thousands of other
SSL VPN or IPSec client remote access Utilizes clientless SSL VPN technology or an easy-to-manage IPSec client for easy access to email, les, computers,
Redundant VPN gateway When using multiple WANs, a primary and secondary VPN can be congured to allow seamless automatic failover
Route-based VPN The ability to perform dynamic routing over VPN links ensures continuous uptime in the event of a temporary VPN
Content/context awareness
Feature Description
User activity tracking User identication and activity are made available through seamless AD/LDAP/Citrix1/TerminalServices SSO
GeoIP country trafc identication
Regular expression DPI ltering Prevents data leakage by identifying and controlling content crossing the network through regular
state synchronization. SonicWall TZ300 and SonicWall TZ400 models support high availability without Active/Standby
synchronization. There is no high availability on SonicWall SOHO models.
feeds to combat advanced threats such as zero-day, malicious insider, compromised credentials, ransomware and
advanced persistent threats.
reliability. Available on SonicWall TZ600 through SonicWall TZ300 models. Optional 802.11 a/b/g/n is available on
SonicWall SOHO models.
a single management console with an intuitive interface to reduce management costs and complexity.
interface and support for SNMPv2/3.
monitoring and reporting with tools such as SonicWall GMSFlow Server or other tools that support IPFIX and NetFlow
with extensions.
site-to-site VPN gateway provisioning between SonicWall rewalls while security and connectivity occurs instantly and
automatically.
large sites, branch ofces or home ofces.
intranet sites and applications from a variety of platforms.
and failback of all VPN sessions.
tunnel failure, by seamlessly re-routing trafc between endpoints through alternate routes.
integration combined with extensive information obtained through DPI.
Identies and controls network trafc going to or coming from specic countries to either protect against attacks from
known or suspected origins of threat activity, or to investigate suspicious trafc originating from the network.
expression matching.
9
Page 10
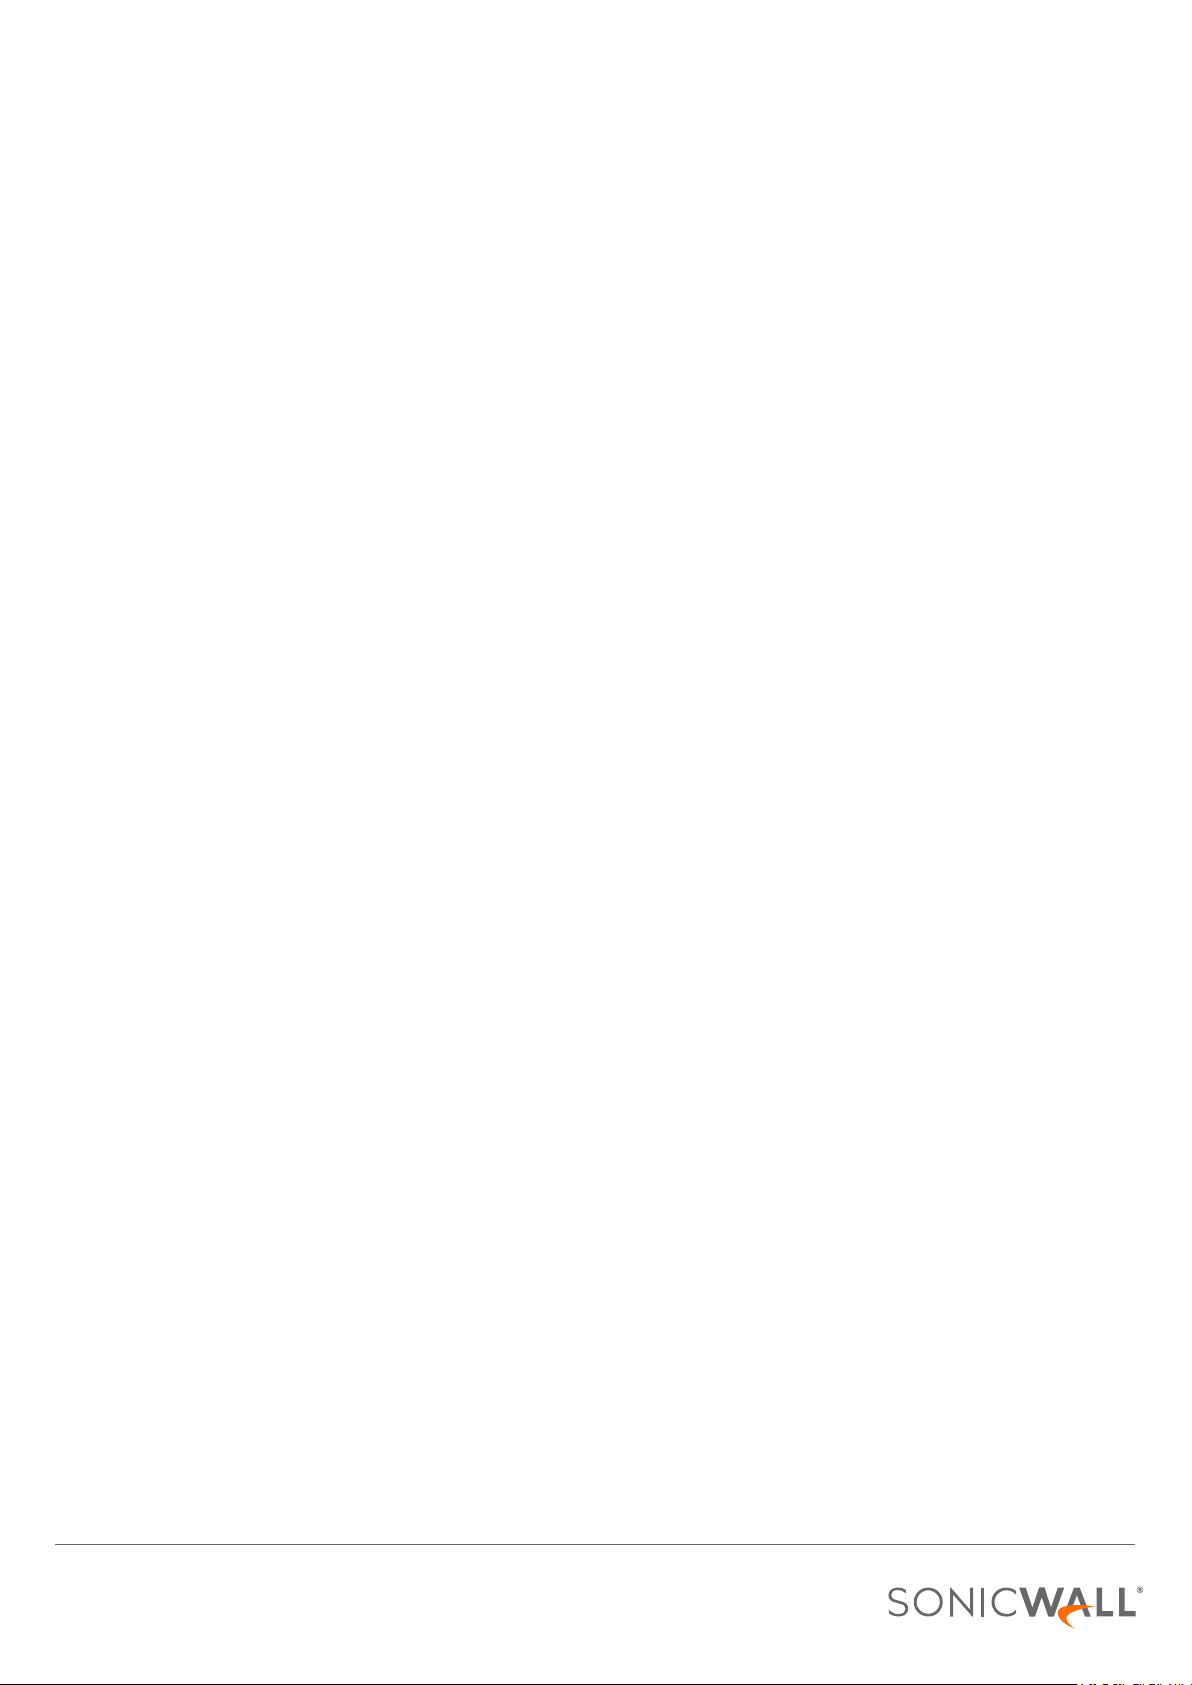
SonicOS feature summary
Firewall
• Stateful packet inspection
• Reassembly-Free Deep Packet
Inspection
• DDoS attack protection
(UDP/ICMP/SY N ood)
• IPv4/IPv6 support
• Biometric authentication for remote
access
• DNS proxy
• Threat API
SSL/SSH decryption and inspection
1
• Deep packet inspection for TLS/SSL/SSH
• Inclusion/exclusion of objects, groups or
hostnames
• SSL control
Capture Advanced Threat Protection
1
• Cloud-based multi-engine analysis
• Virtualized sandboxing
• Hyper visor level analysis
• Full system emulation
• Broad le type examination
• Automated & manual submission
• Real-time threat intelligence updates
• Auto-Block capability
Intrusion prevention
1
• Signature-based scanning
• Automatic signature updates
• Bidirectional inspection
• Granular IPS rule capability
• GeoIP/Botnet ltering
2
• Regular expression matching
Anti-malware
1
• Stream-based malware scanning
• Gateway anti-virus
• Gateway anti-spyware
• Bi-directional inspection
• No le size limitation
• Cloud malware database
Application identication
1
• Application control
• Application visualization
2
• Application component blocking
• Application bandwidth management
• Custom application signature creation
• Data leakage prevention
• Application reporting over NetFlow/
IPFIX
• User activity tracking (SSO)
• Comprehensive application signature
database
Web content ltering
1
• URL ltering
• Anti-proxy technology
• Keyword blocking
• Bandwidth manage CFS rating
categories
• Unied policy model with app control
• Content Filtering Client
VPN
• Auto-provision VPN
• IPSec VPN for site-to-site connectivity
• SSL VPN and IPSec client remote access
• Redundant VPN gateway
• Mobile Connect for iOS, Mac OS X,
Windows, Chrome, Android and
Kindle Fire
• Route-based VPN (OSPF, RIP, BGP)
Networking
• PortShield
• Enhanced logging
• Layer-2 QoS
• Port security
• Dynamic routing (RIP/OSPF/BGP)
• SonicWall wireless controller
• Policy-based routing
(ToS/metric and ECMP)
• Asymmetric routing
• DHCP ser ver
• NAT
• Bandwidth management
• High availability - Active/Standby with
state sync
3
• Inbound/outbound load balancing
• L2 bridge mode, NAT mode
• 3G/4G WAN failover
• Common Access Card (CAC) support
VoIP
• Granular QoS control
• Bandwidth management
• DPI for VoIP trafc
• H.323 gatekeeper and SIP proxy support
Management and monitoring
• Web GUI
• Command line interface (CLI)
• SNMPv2/v3
• Centralized management and reporting
with SonicWall GMS
• Logging
• Netow/IPFix exporting
• Cloud-based conguration backup
• Application and bandwidth visualization
• IPv4 and IPv6 management
• Dell X-Series switch management
including cascaded switches
Integrated Wireless
• Dual-band (2.4 GHz and 5.0 GHz)
• 802.11 a/b/g/n/ac wireless standards
• Wireless intrusion detection and
prevention
• Wireless guest services
• Lightweight hotspot messaging
• Virtual access point segmentation
• Captive portal
• Cloud ACL
2
1
Requires added subscription
2
Not available on SOHO series
3
State sync high availability only on SonicWall TZ50 0 and SonicWall TZ60 0 models
10
Page 11
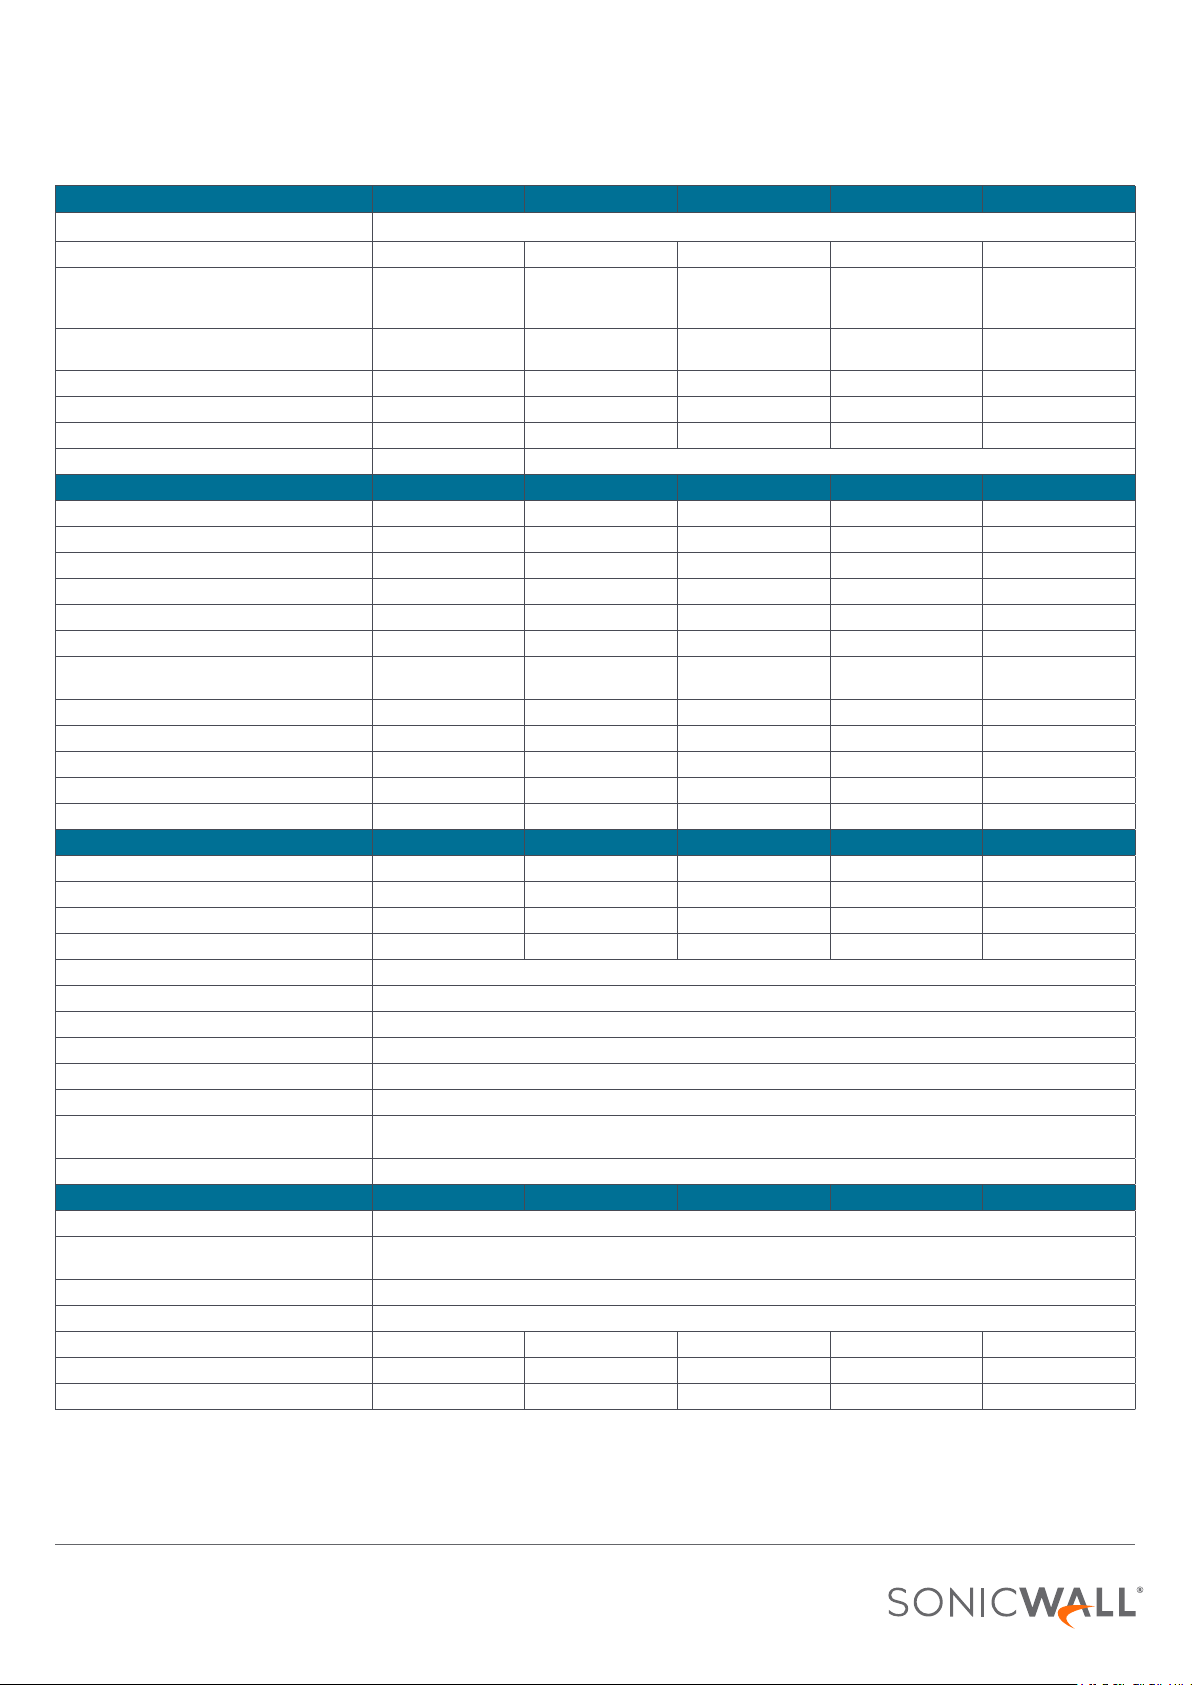
SonicWall TZ series system specications
Hardware overview SOHO series TZ300 series TZ400 series TZ500 series TZ600
Operating system
Security processing cores 2 2 4 4 4
Interfaces 5x1GbE, 1 USB,
1 Console
5x1GbE, 1 USB,
1 Console
Expansion USB USB USB 2 USB Expansion Slot
Single Sign-On (SSO) Users 250 500 500 500 500
VLAN interfaces 25 25 50 50 50
Access points supported (maximum) 2 8 16 16 24
Dell X-Series switch models supported Not available X1008/P, X1018/P, X1026/P, X1052/P, X4012
Firewall/VPN performance SOHO series TZ300 series TZ400 series TZ500 series TZ600
Firewall inspection throughput
Full DPI throughput
2
1
Application inspection throughput
IPS throughput
2
Anti-malware inspection throughput
2
2
300 Mbps 750 Mbps 1,300 Mbps 1,400 Mbps 1,500 Mbps
50 Mbps 100 Mbps 300 Mbps 400 Mbps 500 Mbps
- 300 Mbps 900 Mbps 1,000 Mbps 1,100 Mbps
100 Mbps 300 Mbps 900 Mbps 1,000 Mbps 1,100 Mbps
50 Mbps 100 Mbps 300 Mbps 400 Mbps 500 Mbps
IMIX throughput 60 Mbps 200 Mbps 500 Mbps 700 Mbps 900 Mbps
TLS/SSL inspection and decryption throughput
2
(DPI SSL)
IPSec VPN throughput
3
15 Mbps 45 Mbps 100 Mbps 150 Mbps 200 Mbps
100 Mbps 300 Mbps 900 Mbps 1,000 Mbps 1,100 Mbps
Connections per second 1,800 5,000 6,000 8,000 12,000
Maximum connections (SPI) 10,000 50,000 100,000 125,000 150,000
Maximum connections (DPI) 10,000 50,000 90,000 100,000 125,000
Maximum connections (DPI SSL) 100 500 500 750 750
VPN SOHO series TZ300 series TZ400 series TZ500 series TZ600
Site-to-site VPN tunnels 10 10 20 25 50
IPSec VPN clients (maximum) 1 (5) 1 (10) 2 (25) 2 (25) 2 (25)
SSL VPN licenses (maximum) 1 (10) 1 (50) 2 (100) 2 (150) 2 (200)
Virtual assist bundled (maximum) - 1 (30-day trial) 1 (30-day trial) 1 (30-day trial) 1 (30-day trial)
Encryption/authentication DES, 3DES, AES (128, 192, 256-bit), MD5, SHA-1, Suite B Cryptography
Key exchange Dife Hellman Groups 1, 2, 5, 14
Route-based VPN RIP, OSPF
Certicate support Verisign, Thawte, Cybertrust, RSA Keon, Entrust and Microsoft CA for SonicWall-to- SonicWall VPN, SCEP
VPN features Dead Peer Detection, DHCP Over VPN, IPSec NAT Traversal, Redundant VPN Gateway, Route-based VPN
Global VPN client platforms supported Microsoft
®
Windows Vista 32/64-bit, Windows 7 32/64-bit, Windows 8.0 32/64-bit, Windows 8.1 32/64-bit, Windows 10
NetExtender Microsoft Windows Vista 32/64-bit, Windows 7, Windows 8.0 32/64-bit, Windows 8.1 32/64-bit, Mac OS X 10.4+, Linux
FC3+/Ubuntu 7+/OpenSUSE
®
Mobile Connect Apple
iOS, Mac OS X, Google® Android™, Kindle Fire, Chrome, Windows 8.1 (Embedded)
Security services SOHO series TZ300 series TZ400 series TZ500 series TZ600
Deep Packet Inspection services Gateway Anti-Virus, Anti-Spyware, Intrusion Prevention, DPI SSL
Content Filtering Service (CFS) HTTP URL, HTTPS IP, keyword and content scanning, Comprehensive ltering based on le types such as ActiveX, Java,
Cookies for privacy, allow/forbid lists
Enforced Client Anti-Virus and Anti-Spyware McAfee
Comprehensive Anti-Spam Service Supported
Application Visualization No Yes Yes Yes Yes
Application Control Yes Yes Yes Yes Yes
Capture Advanced Threat Protection No Ye s Ye s Ye s Yes
SonicOS
7x1GbE, 1 USB,
1 Console
®
and Kaspersky
8x1GbE, 2 USB,
1 Console
™
10x1GbE, 2 USB,
1 Console,
1 Expansion Slot
(Rear)*, 2 USB
11
Page 12
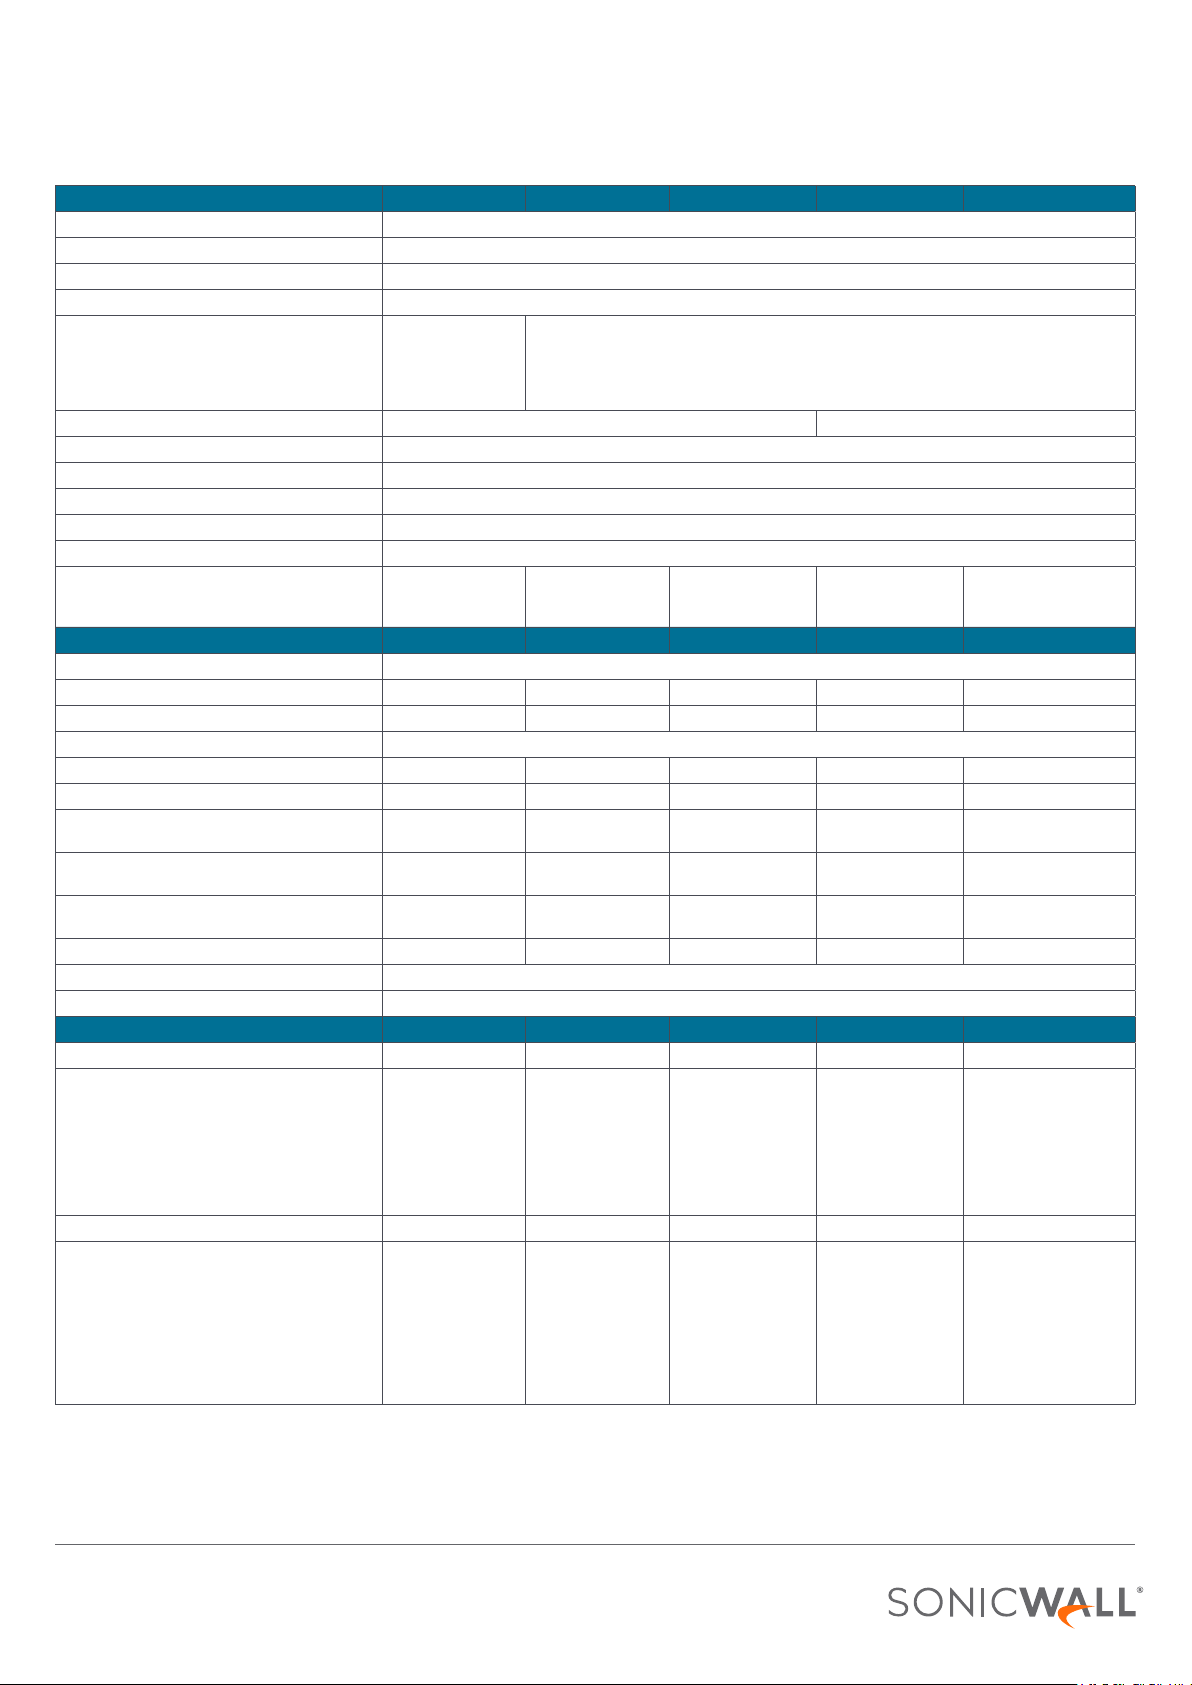
SonicWall TZ series system specications con't
Networking SOHO series TZ300 series TZ400 series TZ500 series TZ600
IP address assignment Static, (DHCP, PPPoE, L2TP and PPTP client), Internal DHCP server, DHCP relay
NAT modes 1:1, 1:many, many:1, many:many, exible NAT (overlapping IPs), PAT, transparent mode
Routing protocols
QoS Bandwidth priority, max bandwidth, guaranteed bandwidth, DSCP marking, 802.1e (WMM)
Authentication LDAP (multiple
Local user database 150 250
VoIP Full H.323v1-5, SIP
Standards TCP/IP, UDP, ICMP, HTTP, HTTPS, IPSec, ISAKMP/IKE, SNMP, DHCP, PPPoE, L2TP, PPTP, RADIUS, IEEE 802.3
Certications FIPS 140-2 (with Suite B) Level 2, UC APL, VPNC, IPv6 (Phase 2), ICSA Network Firewall, ICSA Anti-virus
Certications pending Common Criteria NDPP
Common Access Card (CAC) Supported
High availability No Active/standby Active/standby Active/standby
Hardware SOHO series TZ300 series TZ400 series TZ500 series TZ600
Form factor Desktop
Power supply (W) 24W external 24W external 24W external 36W external 60W external
Maximum power consumption (W) 6.4 / 11.3 6.9 / 12.0 9.2 / 13.8 13.4 / 17.7 16.1
Input power 100 to 240 VAC, 50-60 Hz, 1 A
Total heat dissipation 21.8 / 38.7 BTU 23.5 / 40.9 BTU 31.3 / 47.1 BTU 45.9 / 60.5 BTU 55.1 BTU
Dimensions 3.6x14.1x19cm 3.5x13.4x19cm 3.5x13.4x19cm 3.5x15x22.5cm 3.5x18x28cm
Weight 0.34 kg / 0.75 lbs
WEEE weight 0.80 kg / 1.76 lbs
Shipping weight 1.20 kg / 2.64 lbs
MTBF (years) 58.9/56.1 (wireless) 56.1 54.0 40.8 18.4
Environment (Operating/Storage) 32°-105° F (0°-40° C)/-40° to 158° F (-40° to 70° C)
Humidity 5-95% non-condensing
Regulatory SOHO series TZ300 series TZ400 series TZ500 series TZ600
Regulatory model (wired) APL31-0B9 APL28-0B4 APL28-0B4 APL29-0B6 APL30-0B8
Major regulatory compliance (wired models) FCC Class B, ICES
Regulatory model (wireless) APL41-0BA APL28-0B5 APL28-0B5 APL29-0B7 -
Major regulatory compliance (wireless models) FCC Class B, FCC
4
domains), XAUTH/
RADIUS, SSO,
Novell, internal
user database
0.48 kg / 1.06 lbs
0.94 kg / 2.07 lbs
1.34 kg / 2.95 lbs
Class B, CE (EMC,
LVD, RoHS), C-Tick,
VCCI Class B, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH,
KCC/MSIP
RF ICES Class B,
IC RF CE (R&TTE,
EMC, LVD, RoHS),
RCM, VCCI Class
B, MIC/TELEC, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH
BGP4, OSPF, RIPv1/v2, static routes, policy-based routing
LDAP (multiple domains), XAUTH/RADIUS, SSO, Novell, internal user database,
0.73 kg / 1.61 lbs
0.84 kg / 1.85 lbs
1.15 kg / 2.53 lbs
1.26 kg / 2.78 lbs
1.37 kg / 3.02 lbs
1.48 kg / 3.26 lbs
FCC Class B, ICES
Class B, CE (EMC,
LVD, RoHS), C-Tick,
VCCI Class B, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH,
KCC/MSIP
FCC Class B, FCC
RF ICES Class B,
IC RF CE (R&TTE,
EMC, LVD, RoHS),
RCM, VCCI Class
B, MIC/TELEC, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH
0.73 kg / 1.61 lbs
0.84 kg / 1.85 lbs
1.15 kg / 2.53 lbs
1.26 kg / 2.78 lbs
1.37 kg / 3.02 lbs
1.48 kg / 3.26 lbs
FCC Class B, ICES
Class B, CE (EMC,
LVD, RoHS), C-Tick,
VCCI Class B, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH,
FCC Class B, FCC
RF ICES Class B,
IC RF CE (R&TTE,
EMC, LVD, RoHS),
RCM, VCCI Class
B, MIC/TELEC, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH
Terminal Services, Citrix
KCC/MSIP
with stateful
synchronization
0.92 kg / 2.03 lbs
1.05 kg / 2.31 lbs
1.34 kg / 2.95 lbs
1.48 kg / 3.26 lbs
1.93 kg / 4.25 lbs
2.07 kg / 4.56 lbs
FCC Class B, ICES
Class B, CE (EMC,
LVD, RoHS), C-Tick,
VCCI Class B, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH,
BSMI, KCC/MSIP
FCC Class B, FCC
RF ICES Class B,
IC RF CE (R&TTE,
EMC, LVD, RoHS),
RCM, VCCI Class
B, MIC/TELEC, UL,
cUL, TUV/GS, CB,
Mexico CoC by UL,
WEEE , REACH
stateful synchronization
Class A, CE (EMC, LVD,
Class A, UL cUL, TUV/
by UL, WEEE , REACH,
Active/standby with
1.47 kg / 3.24 lbs
1.89 kg /4.16 lbs
2.48 kg / 5.47 lbs
FCC Class A, ICES
RoHS), C-Tick, VCCI
GS, CB, Mexico CoC
KCC/MSIP
-
12
Page 13
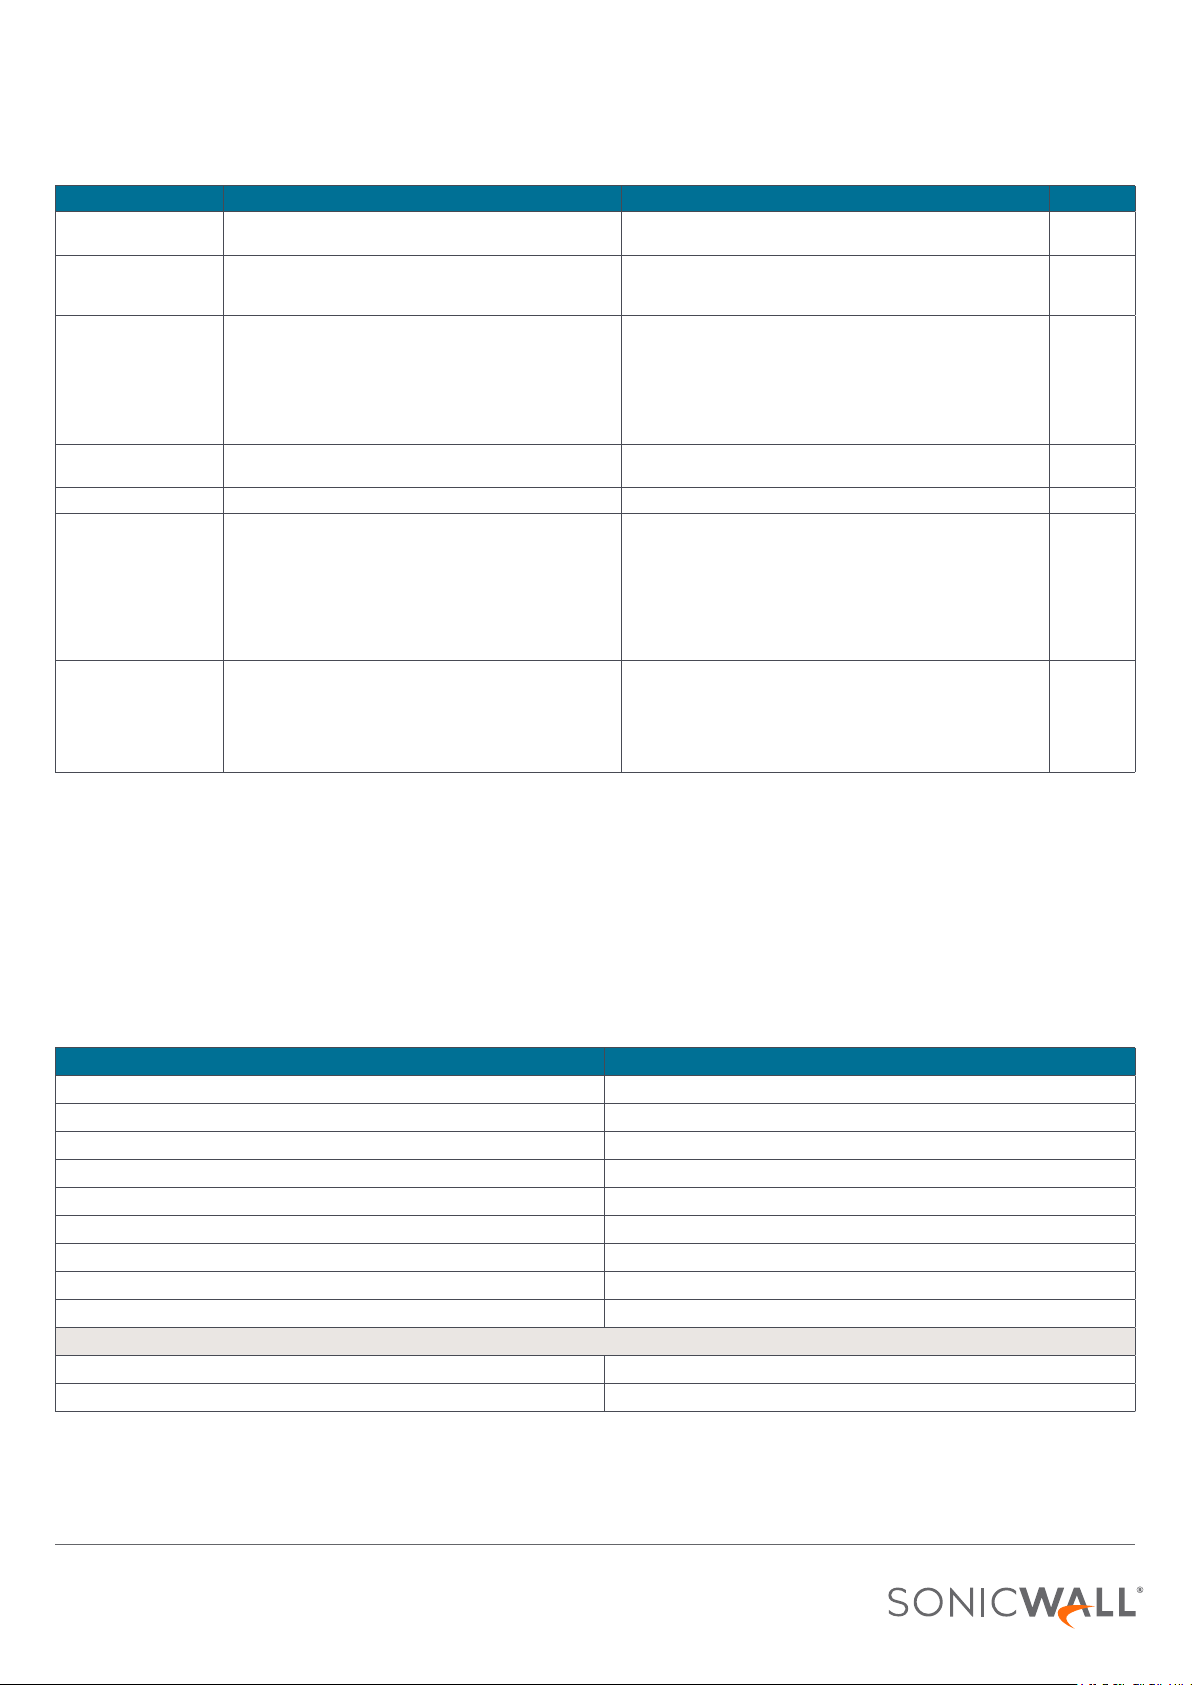
SonicWall TZ series system specications con't
Integrated Wireless SOHO series TZ300, TZ400, TZ500 series TZ600
Standards 802.11 a/b/g/n 802.11a/b/g/n/ac (WEP, WPA, WPA2, 802.11i, TKIP, PSK,02.1x,
Frequency bands
5
Operating Channels 802.11a: US and Canada 12, Europe 11, Japan 4, Singapore
Transmit output power Based on the regulatory domain specied by the system
802.11a: 5.180-5.825 GHz; 802.11b/g: 2.412-2.472 GHz;
802.11n: 2.412-2.472 GHz, 5.180-5.825 GHz;
4, Taiwan 4; 802.11b/g: US and Canada 1-11, Europe 1-13,
Japan 1-14 (14-802.11b only); 802.11n (2.4 GHz): US and
Canada 1-11, Europe 1-13, Japan 1-13; 802.11n (5 GHz):
US and Canada 36-48/149-165, Europe 36-48, Japan 36-48,
Spain 36-48/52-64;
802.11a: 5.180-5.825 GHz; 802.11b/g: 2.412-2.472 GHz;
802.11n: 2.412-2.472 GHz, 5.180-5.825 GHz; 802.11ac: 2.412-
802.11a: US and Canada 12, Europe 11, Japan 4, Singapore 4,
Taiwan 4; 802.11b/g: US and Canada 1-11, Europe 1-13, Japan
1-14 (14-802.11b only); 802.11n (2.4 GHz): US and Canada 1-11,
Europe 1-13, Japan 1-13; 802.11n (5 GHz): US and Canada
36-48/149-165, Europe 36-48, Japan 36-48, Spain 36-48/52-64;
802.11ac: US and Canada 36-48/149-165, Europe 36-48, Japan
Based on the regulatory domain specied by the
administrator
Transmit power control Supported Supported -
Data rates supported 802.11a: 6, 9, 12, 18,24, 36, 48, 54 Mbps per channel;
802.11b: 1, 2, 5.5, 11 Mbps per channel; 802.11g: 6, 9, 12,
18, 24, 36, 48, 54 Mbps per channel; 802.11n: 7.2, 14.4,
21.7, 28.9, 43.3, 57.8, 65, 72.2, 15,30, 45, 60, 90, 120, 135,
150 Mbps per channel;
802.11a: 6, 9, 12, 18, 24, 36, 48, 54 Mbps per channel; 802.11b:
1, 2, 5.5, 11 Mbps per channel; 802.11g: 6, 9, 12, 18, 24, 36, 48,
54 Mbps per channel; 802.11n: 7.2, 14.4, 21.7, 28.9, 43.3, 57.8,
65, 72.2, 15,30, 45, 60, 90, 120, 135, 150 Mbps per channel;
802.11ac: 7.2, 14.4, 21.7, 28.9, 43.3, 57.8, 65, 72.2, 86.7, 96.3,
15, 30, 45, 60, 90, 120, 135, 150, 180, 200, 32.5, 65, 97.5, 130,
195, 260, 292.5, 325, 390, 433.3, 65, 130, 195, 260, 390, 520,
Modulation technology
spectrum
802.11a: Orthogonal Frequency Division Multiplexing
(OFDM); 802.11b: Direct Sequence Spread Spectrum (DSSS);
802.11g: Orthogonal Frequency Division Multiplexing
(OFDM)/Direct Sequence Spread Spectrum (DSSS); 802.11n:
Orthogonal Frequency Division Multiplexing (OFDM)
802.11a: Orthogonal Frequency Division Multiplexing (OFDM);
802.11b: Direct Sequence Spread Spectrum (DSSS); 802.11g:
Orthogonal Frequency Division Multiplexing (OFDM)/Direct
Sequence Spread Spectrum (DSSS); 802.11n: Orthogonal
Frequency Division Multiplexing (OFDM); 802.11ac: Orthogonal
Frequency Division Multiplexing (OFDM)
EAP-PEAP, EAP-TTLS
2.472 GHz, 5.180-5.825 GHz
36-48, Spain 36-48/52-64
system administrator
585, 650, 780, 866.7 Mbps per channel
-
-
-
-
-
-
*Future u se.
1
Testing Methodologies: Maximum performance based on RFC 2544 (for rewall). Actual performance may var y depending on network conditions and activated services.
2
Full DPI/GatewayAV/Anti-Spyware/IPS throughput measured using industry standard Spirent WebAvalanche HTTP per formance test and Ixia test tools. Testing done with
multiple ows through multiple port pairs.
3
VPN throughput measured using UDP trafc at 1280 byte packet size adhering to RFC 2544. All specications, features and availability are subjec t to change.
4
BGP is available only on SonicWall TZ40 0, TZ500 and TZ600.
5
All TZ integrated wireless models can support either 2.4GHz or 5GHz band. For dual-band support, please use SonicWall's wireless access points products (SonicPoints)
SonicWall TZ Series ordering information
Product SKU
SonicWall SOHO with 1-year TotalSecure 01-SSC-0651
SonicWall SOHO Wireless-N with 1-year TotalSecure 01-SSC-0653
SonicWall TZ300 with 1-year TotalSecure 01-SSC-0581
SonicWall TZ300 Wireless-AC with 1-year TotalSecure 01-SSC-0583
SonicWall TZ400 with 1-year TotalSecure 01-SSC-0514
SonicWall TZ400 Wireless-AC with 1-year TotalSecure 01-SSC-0516
SonicWall TZ500 with 1-year TotalSecure 01-SSC-0445
SonicWall TZ500 Wireless-AC with 1-year TotalSecure 01-SSC-0446
SonicWall TZ600 with 1-year TotalSecure 01-SSC-0219
High availability options (each unit must be the same model)
SonicWall TZ500 High Availability 01-SSC-0439
SonicWall TZ600 High Availability 01-SSC-0220
13
Page 14
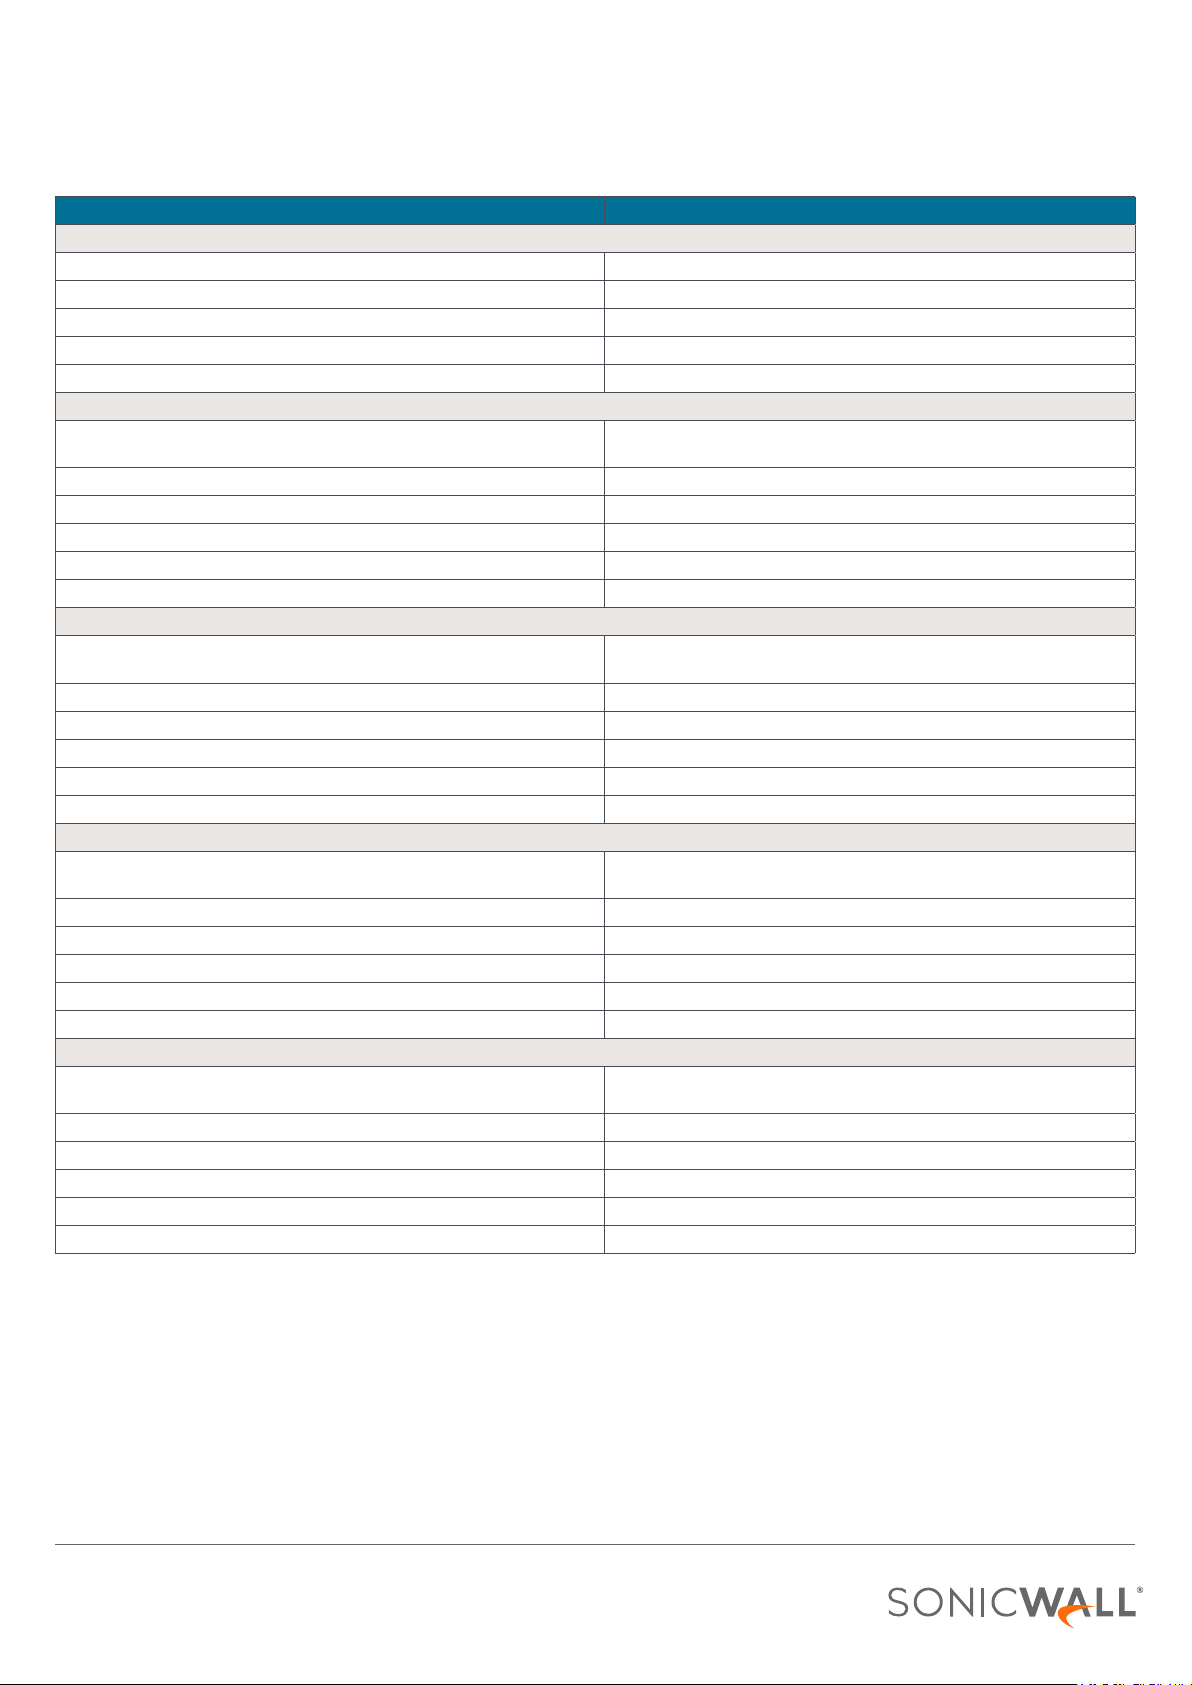
SonicWall TZ Series ordering information con't
Services SKU
For SonicWall SOHO Series
Comprehensive Gateway Security Suite 1-year 01-SSC-0688
Gateway Anti-Virus, Intrusion Prevention and Application Control 1-year 01-SSC-0670
Content Filtering Service 1-year 01-SSC-0676
Comprehensive Anti-Spam Service 1-year 01-SSC-0682
24x7 Support 1-year 01-SSC-0700
For SonicWall TZ300 Series
Advanced Gateway Security Suite – Capture ATP, Threat Prevention,
Content Filtering and 24x7 Support for TZ300 (1-year)
Capture Advanced Threat Protection for TZ300 (1-year) 01-SSC-1435
Gateway Anti-Virus, Intrusion Prevention and Application Control 1-year 01-SSC-0602
Content Filtering Service 1-year 01-SSC-0608
Comprehensive Anti-Spam Service 1-year 01-SSC-0632
24x7 Support 1-year 01-SSC-0620
For SonicWall TZ400 Series
Advanced Gateway Security Suite – Capture ATP, Threat Prevention,
Content Filtering and 24x7 Support for TZ400 (1-year)
Capture Advanced Threat Protection for TZ400 (1-year) 01-SSC-1445
Gateway Anti-Virus, Intrusion Prevention and Application Control 1-year 01-SSC-0534
Content Filtering Service 1-year 01-SSC-0540
Comprehensive Anti-Spam Service 1-year 01-SSC-0561
24x7 Support 1-year 01-SSC-0552
For SonicWall TZ500 Series
Advanced Gateway Security Suite – Capture ATP, Threat Prevention,
Content Filtering and 24x7 Support for TZ500 (1-year)
Capture Advanced Threat Protection for TZ500 (1-year) 01-SSC-1455
Gateway Anti-Virus, Intrusion Prevention and Application Control 1-year 01-SSC-0458
Content Filtering Service 1-year 01-SSC-0464
Comprehensive Anti-Spam Service 1-year 01-SSC-0482
24x7 Support 1-year 01-SSC-0476
For SonicWall TZ600
Advanced Gateway Security Suite – Capture ATP, Threat Prevention,
Content Filtering and 24x7 Support for TZ600 (1-year)
Capture Advanced Threat Protection for TZ600 (1-year) 01-SSC-1465
Gateway Anti-Virus, Intrusion Prevention and Application Control 1-year 01-SSC-0228
Content Filtering Service 1-year 01-SSC-0234
Comprehensive Anti-Spam Service 1-year 01-SSC-0252
24x7 Support 1-year 01-SSC-0246
01-SSC-1430
01-SSC-1440
01-SSC-1450
01-SSC-1460
About Us
SonicWall has been ghting the cyber-criminal industry for over 25 years, defending small, medium size businesses and enterprises
worldwide. Our combination of products and partners has enabled a real-time cyber defense solution tuned to the specic needs of
the more than 500,000 global businesses in over 150 countries, so you can do more business with less fear.
SonicWall, Inc.
5455 Great America Parkway | Santa Clara, CA 95054
Refer to our website for additional information.
www.sonicwall.com
© 2017 SonicWall Inc. ALL RIGHTS RESERVED. SonicWall is a
trademark or registered trademark of SonicWall Inc. and/or its afliates
in the U.S.A. and/or other countries. All other trademarks
and registered trademarks are property of their respective owners.
Datasheet-TZ Series-US-VG-MKTG658
 Loading...