

Page 1
Casa to ARRIS Command Reference
For Commands Containe d in the C100G Lab
May 2016
Page 2
© 2016 Casa Systems, Inc.
All rights reserved. Licensed software products are owned by Casa Systems or its suppliers and are protected by United States
copyright laws and international treaty provisions.
The information regarding the product in this manual is subject to change without notice. All statements, information, and
recommendations in this manual are believed to be accurate but are presented without warranty of any kind, express of implied.
Users must take full responsibility for their application of the product.
In no event shall Casa or its suppliers be liable for any indirect, special, consequential, or incidental damages, including, without
limitation, lost profits or loss or damage to data arising out of the use or inability to use this manual, even if Casa or its suppliers
have been advised of the possibility of such damages.
Page 3
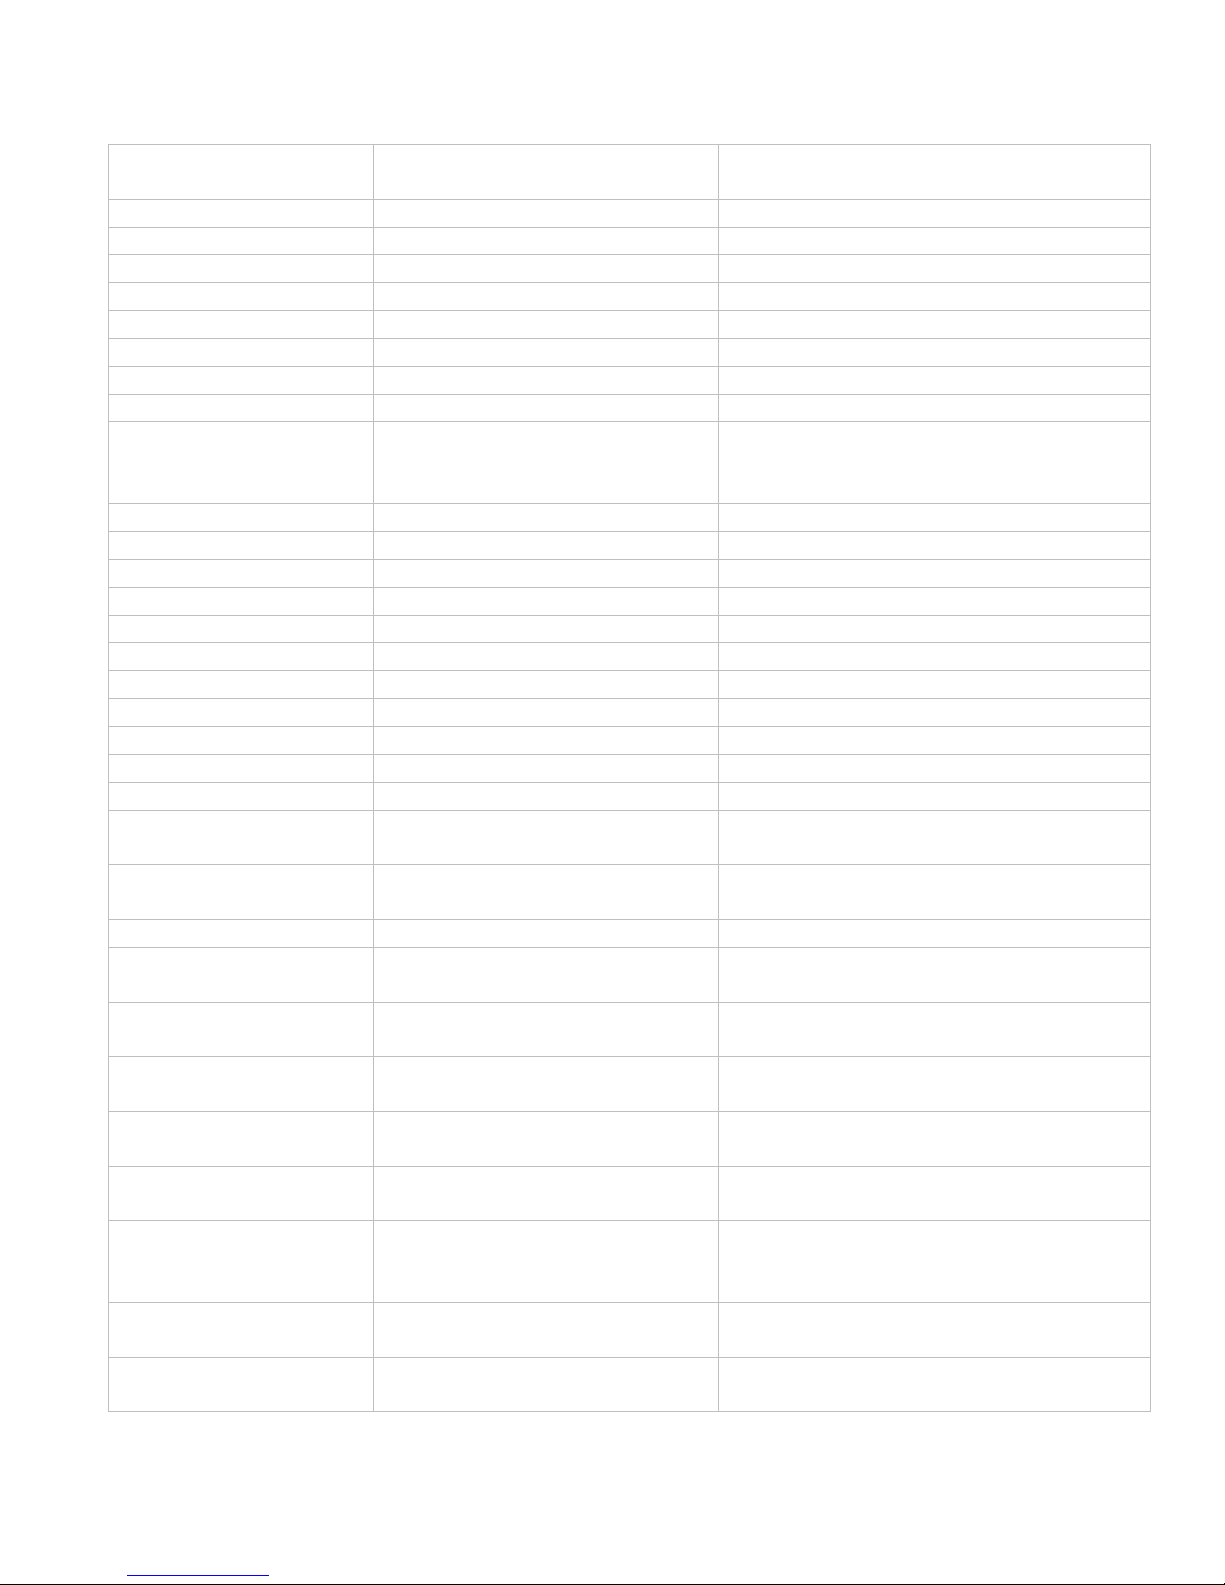
Lab Guide CLI Conversion
Table; Casa to ARRIS
Function
Casa Command
ARRIS Command
show cable modem
show cable modem
show ip route
show ip route
enable
enable
exit
exit
ping <ipaddr>
ping {ipaddr}
show run
show
config
configure
{terminal|memory|network|overwrite-
network}
copy <orig> <dest>
copy <orig> <dest>
copy run start
write [memory|terminal|networkfile|erase]
del <filename>
delete <filename>
del startup-config
erase startup-configuration
Redundancy
High Availability on by default.
CPU Redundancy
SMM HA:
(RSM) Redundancy
show current status
show system
show linecard status
force failover
ha module <module #> protect
Contact ARRIS Technical Support
show sync status
show smm sync-status
I/O Module Redundancy
I/O HA:
CAM Sparing
show current status
show ha configuration
show spare-group
show linecard status
force failover
ha module <module #> protect
configure slot <slot> shutdown
configure slot <slot> no shutdown
Image and File
Management
copy a configuration file
copy nvram startup-config nvram
prep-upgradeX
copy /system/cfgfiles/<filename>
/system/cfgfiles/<newfilename>
show files and directories
ls
dir
show c:[ all | filesys]
tftp config file to server
copy nvram prep-upgradeX tftp
10.4.1.3
copy /system/cfgfiles/<filename>
tftp://<tftpserver ip address>/<filename>
show current software
version
show bootdev
show version detail < 6 | 7 >
show image
ftp a new software version
copy ftp <your username> 10.4.1.3
copy
name> /loads/<image name>
apply a service patch to an
image
system patch apply
classpatch_pb31ba.tgz
patch install <patch file>
remove a patch
remove patch
classpatch_pb31ba.tgz
patch remove <patch file>
to the CCAP
ccsi.gz.rel7.7.0.0_build4479 nvram
ftp://login:password@ftpserverip/<image
1
Page 4
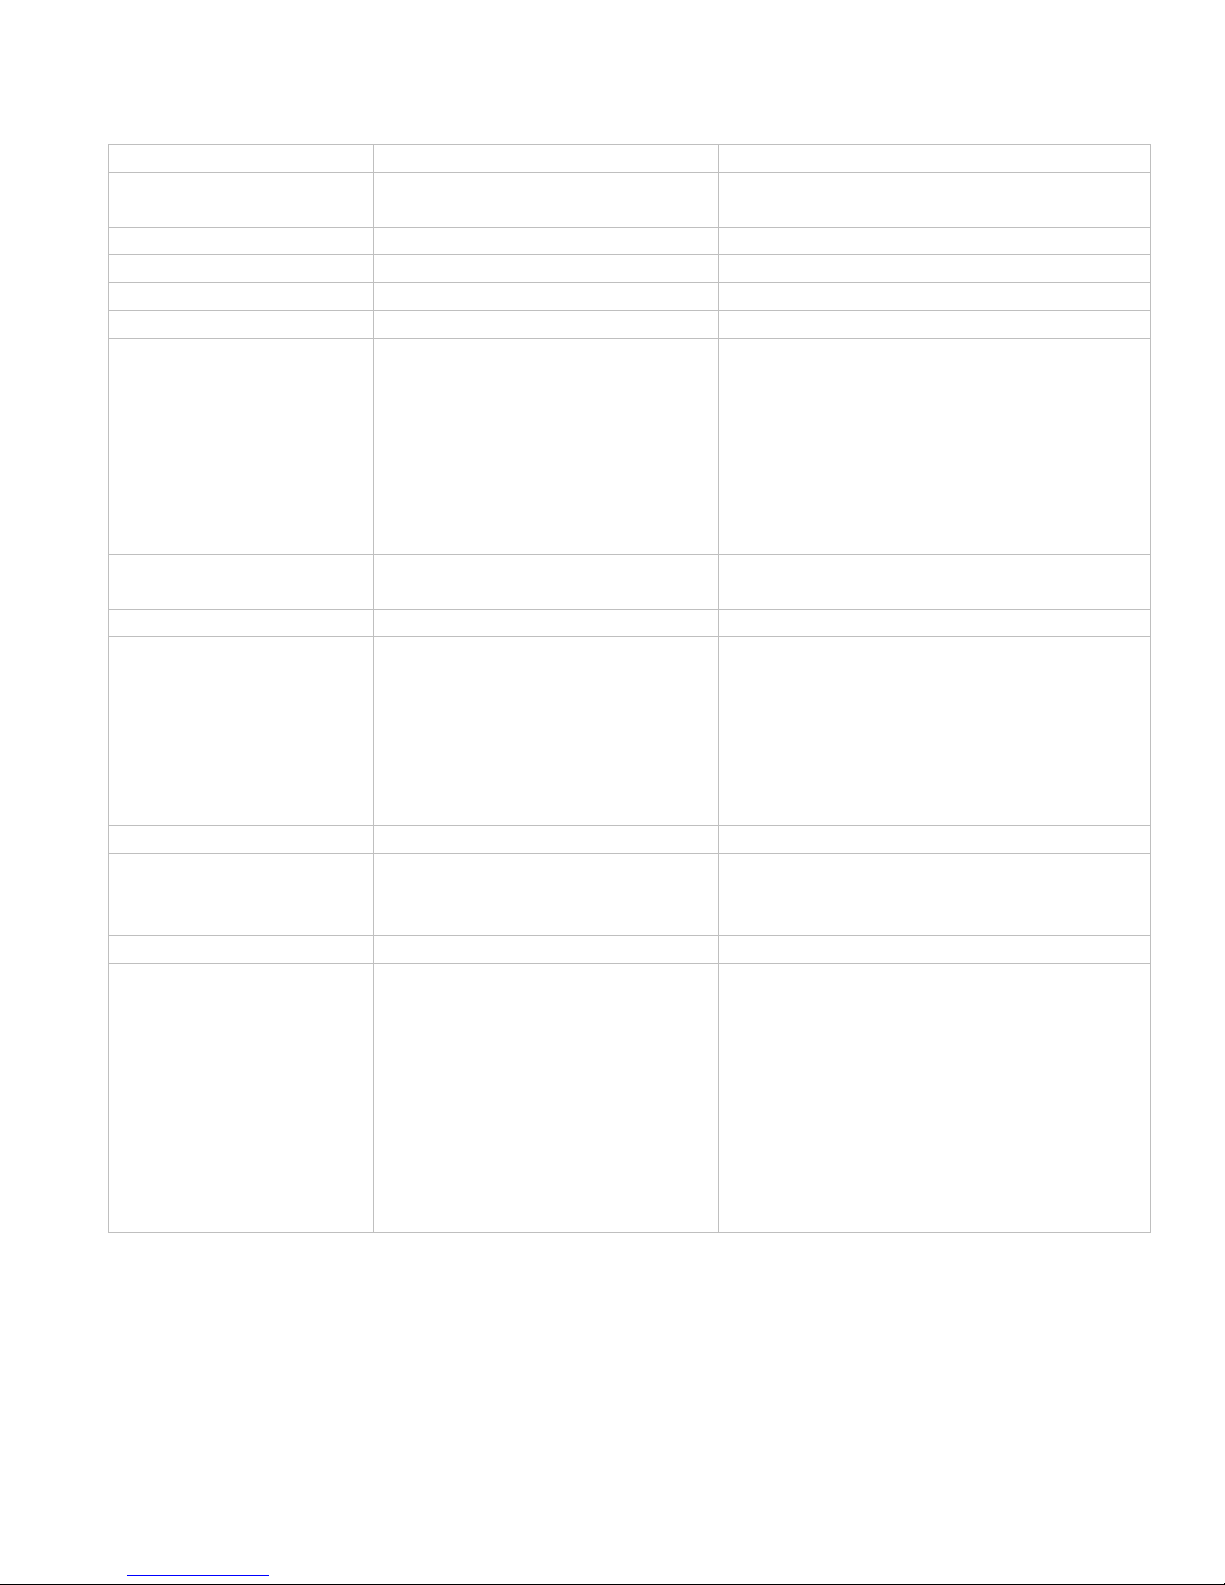
Casa Command
ARRIS Command
configure image to load on
next reboot
system bootdev nvram
ccsi.gz.rel7.7.0.0_build4479
reload <image file>
reload commit
reboot system
system reboot
reload
view system module status
show system
Enable LACP
configure trunking
interface trunk <trunk #>
<interface> mode active
configure interface link-aggregate <0-7> min-
shutdown no
view LACP information
show lacp summary
show lacp [6/7] [{counters \ local \ partner \
sys-id}]
Configure a VLAN with the
interface vlan <vlan id>
no shutdown
Configure a Loopback
interface loopback <#>
255.255.255.255
configure interface loopback <0…13> ip
Configure DHCP Relay for
interface ip-bundle <#>
server ipv6 address>
configure interface cable-mac <mac> cable
<interface> mode active
no shutdown
links <1-8>
configure interface link-aggregate <0-7> lacp
mode enable
configure interface Ethernet <6/7>/<0-7>
link-aggregate <0-7>
configure interface link-aggregate <0-7>
Trunk as an Interface
trunk <trunk #>
ip address <ip address> <mask>
ipv6 address <ipv6 address>/64
bdf interval 100 min_rx 100
multiplier 4
Interface
CMs and CPEs
ip address <loopback ip address>
ip address <ipaddress> <mask>
ip address <ip address> <mask>
secondary
cable helper-address <dhcp server
ip address>
ipv6 address <ipv6 address/mask>
cable helper-ipv6-address <dhcp
address <ipaddress>/32 shutdown no
helper-address <DHCP Server IP address> [
cable-modem | host | cpe | mta | ps | stb |
any ]
2
Page 5
Casa Command
ARRIS Command
Configure OSPF v2
create an OSPF routing
instance
router ospf 1
configure router ospf vrf default router-id
assign routing to a VLAN
interface vlan <vlan id>
end
Configure OSPFv3
configure global OSPv3
router ospf6 1
yes
configure ipv6 router ospf router-id
Verify BFD
verify BFD
show bfd session
show bfd session detail
Verify OSPFv4
verify OSPFv4
show ip ospf
show ip ospf
passive-interface ip-bundle 1
network <network ip>/30 area 0
network <loopback ip address>/32
area 0
network <CM network>/24 area 0
network <CPE subnet>/24 area 0
area 0 authentication messagedigest
log-adjacency-changes
<router id>
configure router ospf [ vrf default ]
network <ip address> <inverse mask>
area <area id>
configure router ospf vrf default
redistribute connected [metric <int>]
[metric-type <type>] [tag <int>]
configure router ospf vrf default no
shutdown
interface
parameters
ip ospf network point-to-point
ipv6 ospf network point-to-point
ipb6 router ospf 1 area 0.0.0.0
ip ospf authentication messagedigest
ip ospf message-digest-key 1 md5
are2@casa
no shutdown
router-id <router id>
redistribute connected
end
end
clear ipv6 ospf process
<router id>
configure ipv6 router ospf redistribute
connected
configure ipv6 router ospf shutdown no
show ip ospf interface vlan <vlan
id>
show ip ospf neighbor detail
show ip ospf database
show ip ospf interface
show ip ospf neighbor
show ip ospf database
3
Page 6
Casa Command
ARRIS Command
Verify OSPFv3
verify OSPFv3
show ipv6 ospf
show ipv6 ospf interface vlan <vlan
show ipv6 ospf
OSPF ASBR Configuration
create a RIP instance
interface ip-bundle 1.2
exit
create an IP Prefix List
ip prefix-list redistribute_rip permit
show ip prefix-list detail
configure ip prefix-list <prefix list name>
create a Route Map
route-map connect_rip_to_ospf
exit
configure route-map <route map name>
redistribute the RIP route
router ospf 1
show this
check your work
show ip ospf database
show ip ospf border-routers
show ip ospf database
id>
show ipv6 ospf neighbor detail
show ipv6 ospf neighbor
show ipv6 route ospf
show ipv6 ospf database
show ipv6 ospf interface [brief]
show ipv6 ospf neighbor [ip address]
[detail]
show ipv6 ospf neighbor
show ipv6 ospf database
ip address <ip address>/24
exit
router rip
network <IP Bundle 1.2 CPE IP
address> 255.255.255.0
172.16.1x.1/24
exit
permit 10
match ip address prefix-list
redistribute_rip
redistribute connected route-map
connect_rip_to_ospf
show ip route
show ip ospf
configure router rip network <network
address>
<ip network/mask>
permit 10 match ip address prefix-list
<prefix list name>
show ip route
show ip ospf
4
Page 7
Casa Commands
ARRIS Commands
IBGP/LDP/MPLS
Configuration
create a VRF table
definition
vrf definition <vrf name>
configure ip vrf <vrf name>
create a network to
interface ip-bundle 1.1
255.255.255.0
configure interface Ethernet 6/1.1 ip
forwarding <vrf name>
enable MPLS and LDP on
interface vlan <vlan id>
enable-ldp ipv4
configure mpls ldp shutdown no
rd 1:1
address-family ipv4
route-target export 1:1
route-target import 1:1
exit
configure vrf <vrf name> routedistinguisher <rd>
configure vrf <vrf name> address-family
ipv4
configure vrf <vrf name> route-target
export <rt>
configure vrf <vrf name> route-target
import <rt>
associate with the VRF
vrf forwarding casalabs
ip address <ip address>
the trunk interface
mpls ip
address <ip address> <mask>
configure interface Ethernet 6/1.1 ip vrf
configure interface Ethernet 6/2 mpls ip
5
Page 8
Casa Commands
ARRIS Commands
create the LDP peering to
your neighbor router
router ldp
configure mpls ldp router-id loopback 1
configure mpls ldp shutdown no
Verify IBGP/LDP/MPLS
verify BGP/MPLS
show ip bgp neighbor
show ip bgp neighbor
Configuring EoMPLS
establish LDP targeted
exit
configure interface ethernet 6/0 mpls ip
create EoMPLS instances
mpls vpws <vpws name>
show mpls vpws xconnect
targeted peer and establishes the VPWS.)
assign cable modem to
show cable modem
show mpls vpws xconnect
Implement parameters in the CM config
router-id <your loopback address>
transport-address ipv4 <your
loopback address>
exit
peers
to each targeted peer
show ip route vrf casalabs
show mpls ldp neighbor
router ldp
targeted-peer ipv4 <peer device IP>
show ldp targeted-peers
peer <peer ip address> <virtual
circuit ID>
exit
show ip route vrf <vrf name>
show mpls ldp neighbors [<IPv4>] [detail]
configure interface ethernet 7/0 mpls ip
configure l2vpn forwarding enable
configure l2vpn cable-mac 1
configure l2vpn cm capability optional
configure mpls ldp router-id loopback 0
configure mpls ldp vc description "vc from
%M on Host %H"
configure mpls ldp neighbor <IPv4>
targeted
configure mpls ldp shutdown no
configure mpls ldp neighbor <IPv4>
targeted
(It appears this command both sets the
each VPWS
cable modem <cm MAC address>
mpls vpnid <vpws name>
clear cable modem reset
file
6
Page 9
Casa command
ARRIS command
Configuring VPLS
establish LDP targeted
peers
exit
configure interface ethernet 6/0 mpls ip
add routers to your BGP
update-source loopback 0
configure vrf <name> auto-import disable
IP address> update-source loopback 1
add routers to your L2VPN
address-family l2vpn vpls
exit-address-family
configure router bgp 64512 address-
establish your VPLS name
and instance identifier
mpls vpls casalab_vpls 1000
configure vrf casalab_vpls auto-import
disable
configure BGP as your
signaling bgp ve-id <ve-id>
exit
add a BPI-enabled cable
modem to the VPLS
cable modem <cm MAC address>
mpls vpnid casalabs_vpls
configure interface cable-mac 101.2 ip
address 195.168.217.254 255.255.255.0
router ldp
targeted-peer ipv4 <peer device IP>
show ldp targeted-peers
configure interface ethernet 7/0 mpls ip
configure l2vpn forwarding enable
configure l2vpn cable-mac 1
configure l2vpn cm capability optional
configure mpls ldp router-id loopback 0
configure mpls ldp vc description "vc from
%M on Host %H"
configure mpls ldp neighbor <IPv4>
targeted
configure mpls ldp shutdown no
instance as neighbors router bgp 64512
address family
signaling protocol
neighbor <neighbor IP address>
remote-as 64512
neighbor <neighbor IP address>
neighbor <neighbor ip address>
activate
neighbor <neighbor ip address>
send-community extended
signaling bgp route-distinguisher
<rd>
signaling bgp route-target <rt>
show this
configure router bgp neighbor <neighbor
IP address> remote-as 64512
configure router bgp neighbor <neighbor
family vpnv4 enable
configure router bgp 64512 addressfamily ipv4 neighbor <neighbor ip
address> activate
configure router bgp 64512
address-family vpnv4 neighbor
<neighbor ip address> activate
configure vrf casalab_vpls rd 100:1
configure vrf
target export 100:1
configure vrf
family ipv4 redistribute
connected
configure vrf
family ipv4 redistribute static
casalab_vpls route-
casalab_vpls address-
casalab_vpls address-
7
Page 10
show mpls vpls casalab_vpls detail
configure interface cable-mac 101.2 cable
SysAdmin Configurations
enable “Save
Configuration” message
system reboot confirm
configure SSH keys
ssh-server gen-hostkey ?
configure crypto key generate dsa
set system time
show timezone list
[timezone]
configure NTP
ntp server 10.4.1.3
ntp sync 10.4.1.3
configure ntp server <ipv4 addr>
configure DNS
nameserver 10.4.1.3
configure ip name-server <server-
configure ip domain-lookup
configure Privileged Mode
password
password <password>
configure enable password <password>
privilege <0-15>
encrypt passwords in
running config
service password-encryption
This is the default on the E6000
add local user
adduser ckent privilege 15
Superman15
configure username <userid> password
<password> privilege <0-15>
delete local user
deluser jimmy
configure no username <userid>
clear cable modem <cm MAC
address>
helper-address 10.10.10.10
configure interface cable-mac 101.2 ip vrf
forwarding CUSTOMER_1
system timezone <string>
system clock <MMDDhhmmYYYY>
show clock
configure clock timezone <timezone
name> | <GMT [+ | -hh[ :mm]]
configure clock set
<yyyy:mm:dd:hh:mm:ss>
show clock [detail] [GMT] [network]
[broadcast] [burst] [key] [manycast]
[maxpoll <4-11>] [minpoll
<4-11>] [multicast] [prefer] [version <24>]
configure ntp server <ipv4 addr> [
broadcast | multicast | manycast ]
address>
8
Page 11
Casa commands
ARRIS commands
create CLI aliases
alias ccm “clear cable modem”
alias cpu “show cpu-process | esc
alias uptime “show cpuinfo all | i
alias ccm clear cable modem
configure local logging
show logging all
logging system errors
show logging
configure logging console 3
configure Syslog
logging host 10.4.1.3
logging source-interface loopback
configure logging host <ip address>
configure SNMP
snmp default
<location>
configure SNMPv2
nmp tgt-addr class-srv2
device location training_lab
00:00:00
alias du “show docsis downstream
channel utilization”
alias scgv “show service group
verbose”
alias scm “show cable modem”
alias scmv “show cable modem
verbose”
up”
alias crs “copy running-config
startup-config”
alias scgv show cable service group
alias scm show cable modem
logging system informational
logging syslog warning
show syslog
snmp community readmibs ro
snmp community letmewrite rw
device contact admin@casasystems.net
device location training_lab
snmpUDPDomain 10.4.1.4 500 1
TrapV2cSNMPv2cTrapsTagList
TrapV2cSNMPv2cTraps nonvolatile 0.0.0.0 500
snmp inform version 2
snmp notify tapUserTrapTagList
tapUserTrapTagList trap nonvolatile
snmp trap-source loopback 0
device contact [email protected]systems.net
configure logging console 7
configure logging syslog 3
show logging syslog
configure snmp-server community
readmibs security rotesting
configure snmp-server community
letmewrite rwtesting
configure snmp-server contact <contact
information string>
configure snmp-server location
9
Page 12
Casa command
ARRIS command
configuring traps
interface docsis-mac 1
cm trap
exit
configure SNMP
snmp community casaadmin rw
configure snmp-server community
create SNMP community
ip access-list limit-snmp
configure PIM traps
ip pim trap invalid-pim-message
cm trap interval 10
configure cable enable-trap
communities
with restricted access to
the MIB tree
snmp community casastudent ro
permit snmp 10.4.1.4
255.255.255.255 <your loopback
IP>
deny snmp any any
exit
show ip access-list limit-snmp
snmp tree-family scout
1.3.6.1.4.1.20858.10.24 – include
non-volatile
snmp access scout-grp – snmpv2c
no-auth exact scout scout scout
non-volatile
snmp security snmpv2c scoutgrpusr scout-grp non-volatile
snmp community imagereader ro
security scoutgrp-usr access-group
limit-snmp
casaadmin security rwtesting
configure snmp-server community
casastudent security rotesting
enable
ip pim trap neighbor-change enable
ip pim trap rp-mapping-change
enable
10
Page 13
Casa commands
ARRIS commands
configuring TACACS+
tacacs-server host 10.4.1.4
tacacs-server key
configure tacacs host 10.4.1.4 key
Access Control Lists
create an access list to
ip access-list restrict-telnet
exit
configure access-list restrict-telnet deny
apply the ACL to your
interface vlan 200
configure interface Ethernet
telnet in
remove the ACL
no ip access-group
configure interface Ethernet
telnet in
bl@hbl@hwh@t3v3r
aaa authentication login default
group tacacsplus
aaa authentication enable default
group tacacsplus enable
aaa authentication login
tacacsplus-local
aaa authorization command 0
default if-authenticated
aaa authorization command 15
default if-authenticated
aaa accounting
aaa accounting commands 0
default stop-only
aaa accounting commands 1
default stop-only
aaa accounting commands 15
default stop-only
aaa tacacs-source loopback 0
bl@hbl@hwh@t3v3r
restrict telnet
VLAN
remark “deny TELNET access to
class-srv2”
deny telnet 10.4.1.4
255.255.255.255 any
ip access-group restrict-telnet
tcp 10.4.1.4 0.0.0.0 eq 23
configure access-list restrict-telnet
remark “deny TELNET access to classsrv2”
<slot>/<port> ip access-group restrict-
<slot>/<port> no ip access-group restrict-
11
Page 14
Casa commands
ARRIS commands
Create a Global Access
Class
create an ACL
ip access-list restrict-ssh
remark “allow ssh only to the
configure access-list restrict-ssh permit
apply the ACL as an access
class
access-class in restrict-ssh
remove the access class
no access-class in
Diagnosing NSI Interface
Issues
diagnose interface issues
show ip interface brief
show iftable eth
show ip interface
diagnose memory issues
show meminfo
show debugging
show memory
diagnose DHCP issues
show dhcp-trace
trace logging dhcp
diagnose High Availability
show ha configuration
show ha switch fault monitor status
diagnose Trunking issues
show lacp summary
show lacp summary
obtain System Information
show bootdev
show envm
show image committed
show environment
diagnose Initialization
show alarm
loopback address”
permit ssh any <your loopback IP
address> 255.255.255.255
deny ssh any any
exit
tcp any eq 22 <your loopback IP address>
0.0.0.0
configure access-list restrict-ssh deny tcp
any eq 22 any
show controller eth
show controller upstream
show controller qam
show cpu-memory process list
show gigabit-rx-cpu-rate
issues
show ha hardware qam 8x96
recovery
Processes
show dmesg
show log
show tech
show controllers ethernet
show controllers cable-upstream
show controllers cable-downstream
show logging
show tech-support
12
Page 15
RFI Configurations
Casa commands
ARRIS commands
configure Downstream
Transmitters (Annex B)
interface qam 0/0
no shutdown
power 550
channel 0 description FNB
channel 0 frequency 555000000 8
no channel 0 shutdown 8
configure interface cable-downstream
0/0 power-level 550
configure interface cable-downstream
0/0/0 description FNB
configure interface cable-downstream
0/0/0 cable frequency 555000000
configure interface cable-downstream
0/0/1 cable frequency 561000000
configure interface cable-downstream
0/0/2 cable frequency 567000000
configure interface cable-downstream
0/0/3 cable frequency 573000000
configure interface cable-downstream
0/0/4 cable frequency 579000000
configure interface cable-downstream
0/0/5 cable frequency 585000000
configure interface cable-downstream
0/0/6 cable frequency 591000000
configure interface cable-downstream
0/0/7 cable frequency 597000000
configure interface cable-downstream
0/0/0 no shutdown
configure interface cable-downstream
0/0/1 no shutdown
configure interface cable-downstream
0/0/2 no shutdown
configure interface cable-downstream
0/0/3 no shutdown
configure interface cable-downstream
0/0/4 no shutdown
configure interface cable-downstream
0/0/5 no shutdown
configure interface cable-downstream
0/0/6 no shutdown
configure interface cable-downstream
0/0/7 no shutdown
13
Page 16
Casa commands
ARRIS commands
configure Upstream
Receivers
show interface upstream brief
show interface upstream brief
configure Downstream
interface qam 0/1
interface upstream 13/0.0
frequency 20000000
no shutdown
no logical-channel 0 shut
interface upstream 13/0.1
frequency 24000000
no shutdown
no logical-channel 0 shutdown
interface upstream 13/0.2
frequency 28000000
no shutdown
no logical-channel 0 shutdown
interface upstream 13/0.3
frequency 32000000
no shutdown
no logical-channel 0 shutdown
configure interface cable-upstream
13/0/0 cable frequency 20000000
configure interface cable-upstream
13/0/0.0 no shutdown
configure interface cable-upstream
13/0/1 cable frequency 24000000
configure interface cable-upstream
13/0/1.0 no shutdown
configure interface cable-upstream
13/0/2 cable frequency 28000000
configure interface cable-upstream
13/0/2.0 no shutdown
configure interface cable-upstream
13/0/3 cable frequency 32000000
configure interface cable-upstream
13/0/3.0 no shutdown
Transmitters (Annex A)
no shutdown
annex A
power 550
channel 0 description FNA
channel 0 frequency 650000000 8
install an Annex A DCAM
configure interface cable-downstream
0/1 power-level 550
configure interface cable-downstream
0/1/0 description FNA
configure interface cable-downstream
0/1/0 cable frequency 655000000
configure interface cable-downstream
0/1/1 cable frequency 663000000
configure interface cable-downstream
0/1/2 cable frequency 671000000
configure interface cable-downstream
0/1/3 cable frequency 679000000
configure interface cable-downstream
0/1/4 cable frequency 687000000
configure interface cable-downstream
0/1/5 cable frequency 695000000
configure interface cable-downstream
0/1/6 cable frequency 703000000
14
Page 17
configure interface cable-downstream
configure Upstream
interface upstream 13/1.0
configure interface cable-upstream
no channel 0 shutdown 8
0/1/7 cable frequency 711000000
configure interface cable-downstream
0/1/0 no shutdown
configure interface cable-downstream
0/1/1 no shutdown
configure interface cable-downstream
0/1/2 no shutdown
configure interface cable-downstream
0/1/3 no shutdown
configure interface cable-downstream
0/1/4 no shutdown
configure interface cable-downstream
0/1/5 no shutdown
configure interface cable-downstream
0/1/6 no shutdown
configure interface cable-downstream
0/1/7 no shutdown
Receivers (Annex A)
frequency 20000000
no shutdown
no logical-channel 0 shutdown
i
nterface upstream 13/1.1
frequency 24000000
no shutdown
no logical-channel 0 shutdown
interface upstream 13/1.2
frequency 28000000
no shutdown
no logical-channel 0 shutdown
interface upstream 13/1.3
frequency 32000000
no shutdown
no logical-channel 0 shutdown
show interface upstream brief
13/1/0 cable frequency 20000000
configure interface cable-upstream
13/1/0.0 no shutdown
configure interface cable-upstream
13/1/1 cable frequency 24000000
configure interface cable-upstream
13/1/1.0 no shutdown
configure interface cable-upstream
13/1/2 cable frequency 28000000
configure interface cable-upstream
13/1/2.0 no shutdown
configure interface cable-upstream
13/1/3 cable frequency 32000000
configure interface cable-upstream
13//3.0 no shutdown
15
Page 18
Casa commands
ARRIS commands
configure DOCSIS MAC
interface for Annex B
interface docsis-mac 1
helper-address x.x.x.x
downstream 1 interface qam 0/0/0
downstream 2 interface qam 0/0/1
downstream 3 interface qam 0/0/2
downstream 4 interface qam 0/0/3
downstream 5 interface qam 0/0/4
downstream 6 interface qam 0/0/5
downstream 7 interface qam 0/0/6
downstream 8 interface qam 0/0/7
upstream 1 interface upstream
13/0.0/0
upstream 2 interface upstream
13/0.1/0
upstream 3 interface upstream
13/0.2/0
upstream 4 interface upstream
13/0.3/0
ip bundle 1
configure interface cable-downstream
0/0/0 type docsis cable-mac 1
configure interface cable-downstream
0/0/1 type docsis cable-mac 1
configure interface cable-downstream
0/0/2 type docsis cable-mac 1
configure interface cable-downstream
0/0/3 type docsis cable-mac 1
configure interface cable-downstream
0/0/4 type docsis cable-mac 1
configure interface cable-downstream
0/0/5 type docsis cable-mac 1
configure interface cable-downstream
0/0/6 type docsis cable-mac 1
configure interface cable-downstream
0/0/7 type docsis cable-mac 1
configure interface cable-upstream
13/0/0 cable cable-mac 1
configure interface cable-upstream
13/0/1 cable cable-mac 1
configure interface cable-upstream
13/0/2 cable cable-mac 1
configure interface cable-upstream
13/0/3 cable cable-mac 1
configure interface cable-mac 1.0 cable
16
Page 19
Casa commands
ARRIS commands
configure DOCSIS MAC
interface for Annex A
interface docsis-mac 2
helper-address x.x.x.x
DOCSIS Security
Configurations
enable Early
Encryption
early-authentication-encryption
enable TFTP Proxy/TFTP
tftp enforce
configure interface cable-mac <mac>
| reject}
enable BPI enforce
cable privacy bpi-enforce
mandatory
configure interface cable-mac <mac>
cable privacy mandatory bpi-plus
downstream 1 interface qam 0/1/0
downstream 2 interface qam 0/1/1
downstream 3 interface qam 0/1/2
downstream 4 interface qam 0/1/3
downstream 5 interface qam 0/1/4
downstream 6 interface qam 0/1/5
downstream 7 interface qam 0/1/6
downstream 8 interface qam 0/1/7
upstream 1 interface upstream
13/2.0/0
upstream 2 interface upstream
13/2.1/0
upstream 3 interface upstream
13/2.2/0
upstream 4 interface upstream
13/2.3/0
ip bundle 1
configure interface cable-downstream
0/1/0 type docsis cable-mac 2
configure interface cable-downstream
0/1/1 type docsis cable-mac 2
configure interface cable-downstream
0/1/2 type docsis cable-mac 2
configure interface cable-downstream
0/1/3 type docsis cable-mac 2
configure interface cable-downstream
0/1/4 type docsis cable-mac 2
configure interface cable-downstream
0/1/5 type docsis cable-mac 2
configure interface cable-downstream
0/1/6 type docsis cable-mac 2
configure interface cable-downstream
0/1/7 type docsis cable-mac 2
configure interface cable-upstream
13/0/0 cable cable-mac 2
configure interface cable-upstream
13/0/1 cable cable-mac 2
configure interface cable-upstream
13/0/2 cable cable-mac 2
configure interface cable-upstream
13/0/3 cable cable-mac 2
configure interface cable-mac 2.0 cable
Authentication and
ranging
Enforce
mandatory
cable privacy bpi-plus-enforce
cable tftp-enforce
configure interface cable-mac <mac>
cable dynamic-secret {block | lock | mark
cable privacy mandatory
configure interface cable-mac <mac>
17
Page 20
Casa commands
ARRIS commands
PHY and DOCSIS MAC Best
Practices
configure Static MAP
Advance
map-advance static 200
configure Interleave level
interleave 16
configure interface cable-downstream
0/0/0 cable interleave-depth 16
enable pre-equalization
auto reset
logical-channel 0 pre-equalization
auto-reset
Modulation Profiles
examine current
Modulation Profiles
show modulation-profile
profile
configure a Modulation
modulation-profile 6
show interface upstrea 13/0.0 | in
Profile
request atdma qpsk off 64 0 16 338
0 16 fixed on 1 1536 qpsk0
initial atdma qpsk off 640 5 34 338
0 48 fixed on 1 1536 qpsk0
station atdma qpsk off 384 5 34 338
0 48 fixed on 1 1536 qpsk0
a-short atdma qpsk off 104 12 75
338 13 8 shortened on 0 2048
qpsk1
a-long atdma qpsk off 104 16 223
338 0 8 shortened on 0 2048 qpsk1
configure cable modulation profile 6 iuc
request mod qpsk prelen 64 diff false fectbytes 16 seed 338 burst-len 0 scrambler
true guard-time-size 16 int-depth 1536
pre-type qpsk0 docsis-mode atdma
configure cable modulation profile 6 iuc
initial mod qpsk prelen 640 diff false fectbytes 5 seed 338 burst-len 0 scrambler
true guard-time-size 48 int-depth 1 intblocksize 1536 pre-type qpsk0 docsismode atdma
configure cable modulation profile 6 iuc
station mod qpsk prelen 385 diff false fectbytes 5 seed 338 burst-len 0 scrambler
true guard-time-size 48 int-depth 1 intblocksize 1536 pre-type qpsk0 docsismode atdma
configure cable modulation profile 6 iuc
a-short mod qpsk prelen 104 diff false
fec-tbytes 12 seed 338 burst-len 13
scrambler true guard-time-size 8 intdepth 2048 pre-type qpsk1 docsis-mode
atdma
configure cable modulation profile 6 iuc
a-long mod qpsk prelen 104 diff false fectbytes 16 seed 338 burst-len 0 scrambler
18
Page 21
true guard-time-size 8 int-depth 2048
atdma | tdma-atdma>]
Small Signal
Compensation
enable Small Signal
Compensation
small-signal-compensation
ugs atdma qpsk off 104 16 223 338
0 8 shortened on 0 2048 qpsk1
pre-type qpsk1 docsis-mode atdma
configure cable modulation profile 6 iuc
augs mod qpsk prelen 104 diff false fectbytes 223 seed 338 burst-len 0 scrambler
true guard-time-size 8 int-depth intblocksize 2048 pre-type qpsk1 docsismode atdma
configure cable modulation-profile <id>
iuc <interval usage code> [mod <qpsk
|qam8
|qam16|qam32|qam64|qam128>] [prelen <preamble len>] [diff <true|false>]
[fec-tbytes <no of bytes>]
[fec-len <FEC code word length>] [seed
<scrambler seed>] [burst-len <max burst
len>] [last-cw
<true|false>] [scrambler <true|false>]
[guard-time-size <0|8–96|no>] [int-depth
<depth>]
[int-blocksize <blocksize>] [pre-type
<preamble type>] [tcm <on|off>] [intstepsize <stepsize>]
[spreader <on |off>] [subframe-code
<subframe size>] [docsis-mode <tdma |
19
Page 22
Casa commands
ARRIS commands
Load Balancing and
Channel Bonding
Configurations
configure Service Groups
service group CCAPx_FNA
MAC Domain Cable Modem Service
enable Load Balancing
load-balance enable
show load-balance static
configure cable load-balance enable
show cable load-balance
upstream 13/0.0
upstream 13/0.1
upstream 13/0.2
upstream 13/0.3
qam 0/0/0
qam 0/0/1
qam 0/0/2
qam 0/0/3
qam 0/0/4
qam 0/0/5
qam 0/0/6
qam 0/0/7
load-balance execution-rule 1
method modem
method utilization dynamic
threshold load 10 enforce 20
minimum 20 dynamic minimum 60
load-balance policy 1
rule execution 1
load-balance general-group defaultsettings
enable
initial-tech broadcast-ranging
policy-id 1
clear cable modem reset
Groups (MD-CM-SGs) are calculated
automatically by the E6000 CER based on
the channel-to-fibernode and channel-toMAC-domain provisioning. The E6000 CER
will automatically create a general load
balancing group for each MAC DomainCable Modem-Service Group (MD-CMSG).
configure cable load-balance generalgroup-defaults init-technique ranging
No matching ARRIS capability. Dynamic
load balancing is based on % of load, not
on number of modems.
20
Page 23
Casa commands
ARRIS commands
Channel Bonding
confirm Bonding
Note: channel bonding is enabled by
default in any intersection of a
Note: channel bonding must be explicitly
Partial Service
configure Partial Service
cable cm-status-report event-list
ranging
impaired-ack
CCAP/CM Diagnostics
display statistics for RFI
show interface qam brief
show interface cable
DOCSIS MAC domain and a service
group.
show cable modem
show cable modem bonding
show downstream channel set
show upstream channel set
enabled with the commands below.
configure interface cable-mac 1
cable dynamic-rcc
configure interface cable-mac 1
cable downstream-bonding-group
dynamic enable
configure interface cableupstream 1/0/0 cable supervis ion
12/0/0-3
configure interface cableupstream 1/0/1 cable supervision
12/0/0-3
configure interface cableupstream 1/0/2 cable supervision
12/0/0-3
configure interface cableupstream 1/0/3 cable supervision
12/0/0-3
show cable bonding-group-status
show cable channel-sets
best practices
interfaces
1,4,7,8
show cable modem cm-status log
cable partial-service continue-
show interface qam stat
show interface upstream brief
show interface upstream stat
configure cable global recover-US-
show interface cable-mac [<mac>] bitrate
show interface cable-upstream
21
Page 24
Casa commands
ARRIS commands
Diagnostic Mode Interface
Commands
check gige interface errors
show module 0 stat gige
show memory on a
downstream module
show module <module #> stat
himem
show memory <slot> detail
show downstream card
statistics
show module <module #> stat qam
show upstream card
statistics
show interface upstream 13/0.0
stat
enable logging of
debugging messges
logging debugging
turn on CM debugging
debug cable macaddress <mac
address>
debug cable
trace logging modem <mac address>
turn off logging and
debugging
no logging
no debug cable
clear logging debug
Cable Modem Show
Commands
show cable modem
show cable modem
clear cable modem <mac address>
reset
verbose
clear cable modem <mac address>
show cable modem verbose
show cable modem mac
show cable modem verbose | inc
Stn
show cable modem verbose | inc
US
show cable modem verbose | inc
DS
show cable modem verbose | inc
Online
show cable modem counters
show cable modem errors
show cable modem dropped
show docsis downstream channel
utilization
show cable modem docsis-mac 1
service-group FNA downstream
throughput
show upstream signal-quality
show spectrum upstream 13/0
show upstream burst-noise
show cable modem partial service
show cable modem detail
show cable modem summary mac
show cable modem errors
show cable modem dropped
show cable modem bonded-impaired
22
Page 25
Casa commands
ARRIS commands
Remote Query
perform a Remote Query
cable modem remote-query 30
show cable modem remote-query
immediate
configure cable modem remote-query 30
DOCSIS Ping
issue a DOCSIS ping
ping docsis <mac address>
ping docsis <mac address>
Cable Flap List
configure the Cable Flap
show cable flap-list config
show cable flap-list
show cable modem phy
immediate
show cable modem <mac address |
ip address> remote-query verbose
list
cable flap-list power-adjust
threshold 1
cable flap-list miss threshold 7
cable flap-list insertion-time 90
configure cable flap-list power-adjust
threshold 10
configure cable flap-list insertion-time 90
23
Page 26
100 Old River Road Suite 100
Andover, MA 01810
978-688-6706
Casa Educational Services
© 2016 Casa Systems, Inc.
All rights reserved.
USA
 Loading...