

Page 1
SmartSwitch Router
User Reference Manual
9032578
Page 2
Page 3
Notice
Cabletron Systems reserves the right to make changes in specifications and ot her information co ntained
in this document without prior notice. The reader should in all cases consult Cabletron Systems to
determine whether any such changes have been made.
The hardware, firmware, or software described in this manual is subject to change without notice.
IN NO EVENT SHALL CABLETRON SYSTEMS BE LIABLE FOR ANY INCIDENTAL,
INDIRECT, SPECIAL, OR CONSEQUENTIAL DAMAGES WHATSOEVER (INCLUDING BUT
NOT LIMITED TO LOST PROFITS) ARISING OUT OF OR RELATED TO THIS MANUAL OR
THE INFORMATION CONTAINED IN IT, EVEN IF CABLETRON SYSTEMS HAS BEEN
ADVISED OF, KNOWN, OR SHOULD HAVE KNOWN, THE POSSIBILITY OF SUCH
DAMAGES.
© Copyright April 1998 by:
Cabletron Systems, Inc.
35 Industrial Way
Rochester, NH 03867-5005
All Rights Reserved
Printed in the United States of America
Order Number:9032578
LANVIEW is a registered trademark, and SmartSwitch is a trademark of
Cabletron Systems, Inc.
CompuServe is a registered trademark of CompuServe, Inc.
i960 microprocessor is a registered trademark of Intel Corp.
Ethernet is a trademark of Xerox Corporation.
SSR User Reference Manual iii
Page 4
Notice
FCC Notice
This device complies with Part 15 of the FCC rules. Operation is subject to the following two
conditions: (1) this device may not cause harmful interference, and (2) this device must accept any
interference received, including interference that may cause undesired operation.
NOTE: This equipment has been tested and found to comply with the limits for a Class A digital
device, pursuant to P art 1 5 of the FCC r ules. These limits are design ed to provide reasonable protection
against harmful interference when the equipment is operated in a commercial environment. This
equipment uses, generates, and can radiate radio frequency energy and if not installed in accordance
with the operator’s manual, may cause harmful interference to radio commu nications. Oper ation of this
equipment in a residential area is likely to cause interference in which case the user will be required to
correct the interference at his own expense.
WARNING: Changes or modifications made to this device which are not expressly approved by the
party responsible for compliance could void the user’s authority to operate the equipment.
VCCI Notice
This is a Class A product based on the standard of the Voluntary Control Council for Interference by
Information Technology Equipment (VCCI). If this equipment is used in a domestic environment, radio
disturbance may arise. When such trouble occurs, the user may be required to take corrective actions.
DOC Notice
This digital apparatus does not exceed the Class A limits for radio noise emissions from digital
apparatus set out in the Radio Interference Regulations of the Canadian Department of
Communications.
Le présent appareil numérique n’émet pas de bruits radioélectriques dépassant les limites applicables
aux appareils numériques de la class A prescrites dans le Règlement sur le brouillage radioélectrique
édicté par le ministère des Communicati o ns du Canada.
iv
Page 5
DECLARATION OF CONFORMITY
ADDENDUM
Application of Council Directive(s): 89/336/EEC
73/23/EEC
Manufacturer’s Name: Cabletron Systems, Inc.
Manufacturer’s Address: 35 Industrial Way
PO Box 5005
Rochester, NH 03867
European Representative Name: Mr. J. Solari
European Representative Address: Cabletron Systems Limited
Nexus House, Newbury
Business Park
London Road, Newbury
Berkshire RG13 2PZ, England
Conformance to Directive(s)/Product Standards:
EC Directive 89/336/EEC
EC Directive 73/23/EEC
EN 55022
EN 50082-1
EN 60950
Equipment Type/Environment: Networking Equipment, for
use in a Commercial or Light
Industrial Environment.
We the undersigned, hereby declare, under our sole responsibility, that the equipment
packaged with this notice conforms to the above directives.
Manufacturer Legal Representative in Europe
Mr. Ronald Fotino Mr. J. Solari
____________________________________________________ ____________________________________
Full Name Full Name
Principal Compliance Engineer Managing Director - E.M.E.A.
____________________________________________________ ____________________________________
Title Title
Rochester, NH, USA Newbury, Berkshire, England
____________________________________________________ ____________________________________
Location Location
SSR User Reference Manual v
Page 6
Notice
vi
Page 7
About This Manual
This manual provides detailed information and procedures for configuring the 8-slot
SmartSwitch Router (SSR-8) software. If you have not yet installed the SSR, use the
instructions in the SmartSwitch Router Getting Started Guide to install the chassis and
perform basic setup tasks, then return to this manual for more detail ed configuration
information.
Who Should Read This Manual?
Read this manual if you are a network administrator responsible for configuring and
monitoring the SSR.
Preface
Page 8
About This Manual
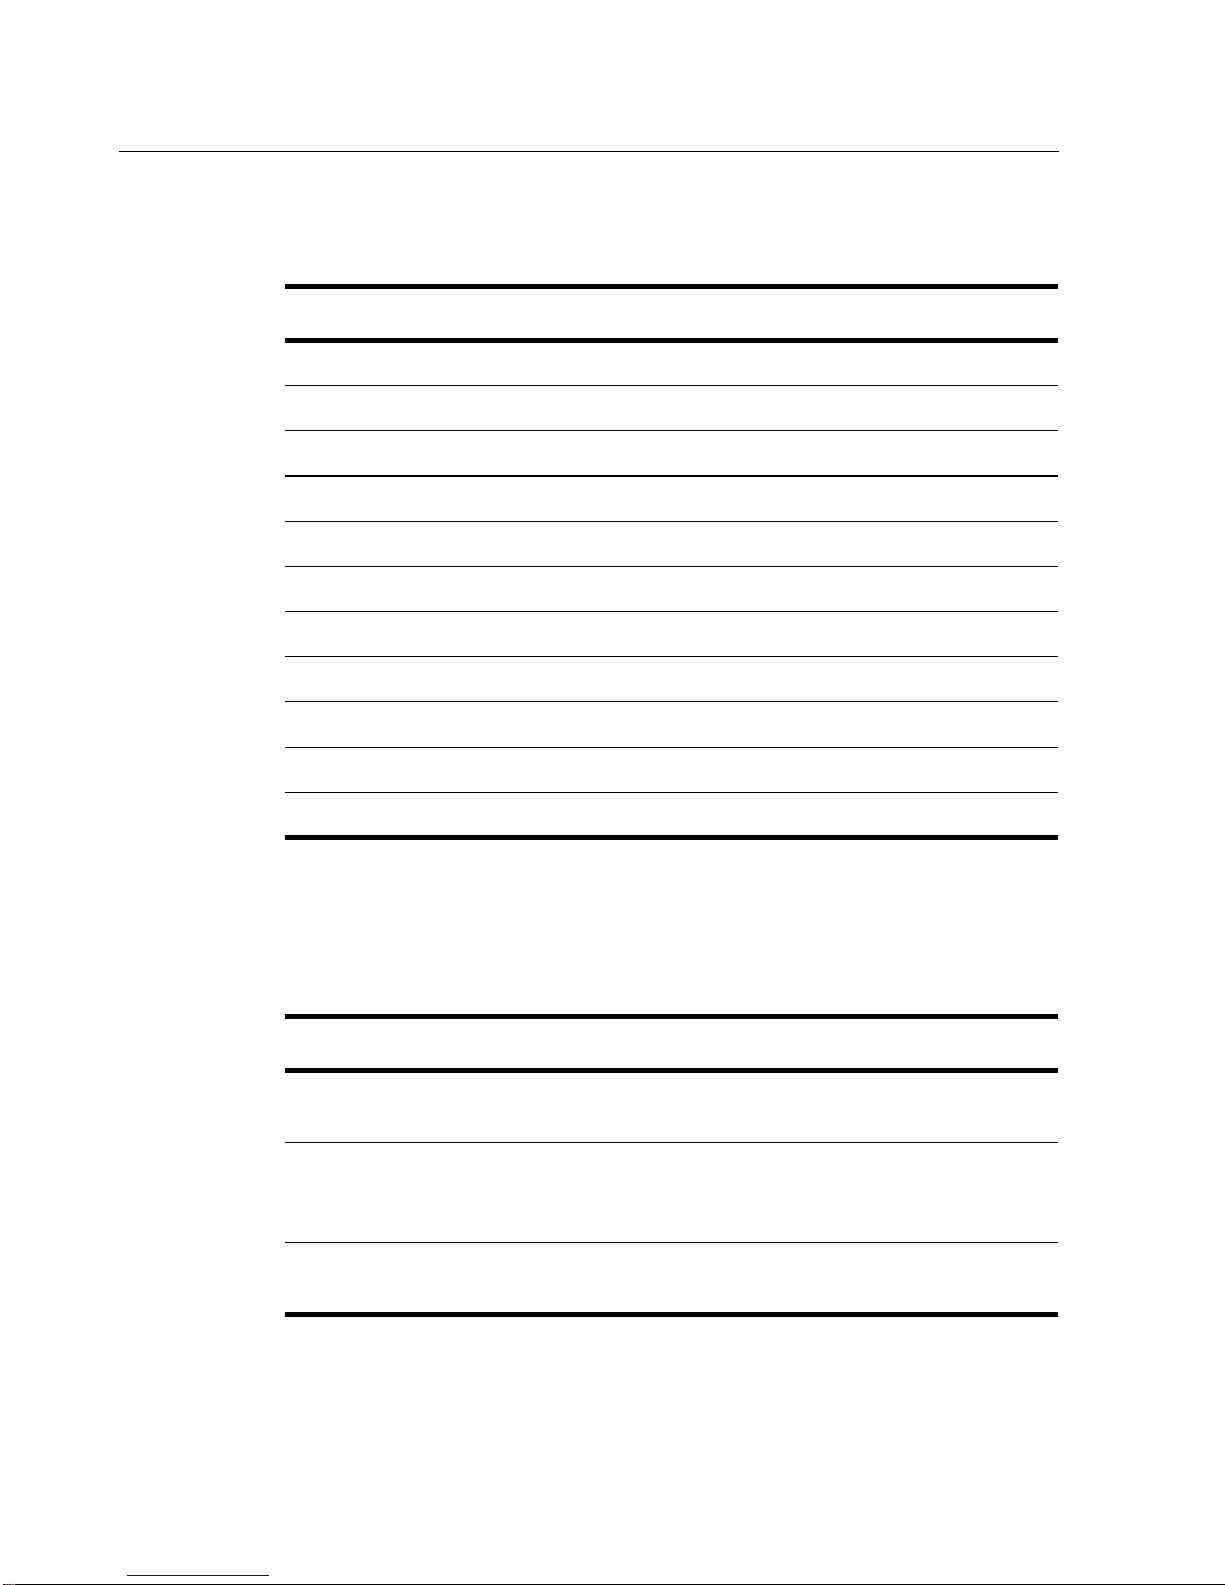
How to Use This Manual
If Yo u Want To... See...
Read overview information Chapter 1
Configure bridging Chapter 2
Configure IP interfaces and global routing parameters Chapter 3
Configure RIP routing Chapter 4
Configure OSPF routing Chapter 5
Configure Routin g Pol ic ie s Chapter 6
Configure IP Multicast routing Chapter 7
Configure IPX routing C hapter 8
Configure filters Chapter 9
Configure QoS (Quality of Service) parameters Chapter 10
Monitor performance Chapter 11
Related Documentation
The Cabletron Systems documentation set includes the following items. R efer to these
other documents to learn more about your product.
For Information About... See the...
Installing and setting up the SSR SmartSwitch Router Getting Started
Managing the SSR using Cabletron
Systems’ element management application
The complete syntax for all CLI commands
Guide
CoreWatch User’s Manual and the
CoreWatch online help
SmartSwitch Router Command Line
Interface Reference Manual
viii SSR User Reference Manual
Page 9
About This Manual
For Information About... See the...
System messages and SNMP traps SmartSwitch Router Error Messag e Ref-
erence Manual
SSR User Reference Manual ix
Page 10
About This Manual
x SSR User Reference Manual
Page 11
Contents
Chapter 1 SmartSwitch Router Product Overview
Supported Media (Encapsulation Type). . . . . . . . . . . . . . . . . . . 1-2
Supported Routing Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-2
Configuring the Cabletron SmartSwitc h Router . . . . . . . . . . . . . 1-3
Understanding the Command Line Interface . . . . . . . . . . . . 1-3
Basic Line Editing Commands . . . . . . . . . . . . . . . . . . . . . . . 1-3
Access Modes . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-4
User Mode . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-5
Enable Mode . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-6
Configure Mode . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-7
Boot PROM Mode . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-8
Disabling a Function or Feature . . . . . . . . . . . . . . . . . . . . . . 1-9
Loading System Images and Configuration Files. . . . . . . . . . . . 1-9
Boot and System Image. . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-9
Configuration Files . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-9
Loading System Image Software . . . . . . . . . . . . . . . . . . . . 1-10
Loading Boot PROM Software . . . . . . . . . . . . . . . . . . . . . . 1-11
Activate the Configuration Commands in the Scratchpad . 1-12
Copy the Configuration to the Startup Configuration File. . 1-13
Managing the SSR. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-13
Set SSR Name. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-14
Set SSR Date and Time. . . . . . . . . . . . . . . . . . . . . . . . . . . 1-14
Configure the SSR CLI. . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-14
Configure SNMP Services . . . . . . . . . . . . . . . . . . . . . . . . . 1-14
Configure DNS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-15
Configure HTTP Services. . . . . . . . . . . . . . . . . . . . . . . . . . 1-15
Monitoring Configuration . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1-15
Chapter 2 Bridging Configuration Guide
Bridging Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-1
Page 12
Contents
Spanning Tree (IEEE 802.1d) . . . . . . . . . . . . . . . . . . . . . . . 2-1
Bridging Modes (Flow-Based and Address-Based) . . . . . . . 2-1
VLAN Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-2
SSR VLAN Support . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-3
VLANs and the SSR. . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-4
Ports, VLANs, and L3 Interfaces . . . . . . . . . . . . . . . . . . 2-4
Access Ports and Trunk Ports (802.1Q support) . . . . . . 2-5
Explicit and Implicit VLANs. . . . . . . . . . . . . . . . . . . . . . . 2-5
Configuring SSR Bridging Functions . . . . . . . . . . . . . . . . . . . . . 2-6
Configure Address-based or Flow-based Bridging. . . . . . . . 2-6
Configuring Spanning Tree . . . . . . . . . . . . . . . . . . . . . . . . . 2-7
Adjust Spanning-Tree Parameters . . . . . . . . . . . . . . . . . . . . 2-7
Set the Bridge Priority. . . . . . . . . . . . . . . . . . . . . . . . . . . 2-8
Set a Port Priority . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-8
Assign Port Costs. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-8
Adjust Bridge Protocol Data Unit (BPDU) Intervals . . . . 2-8
Configuring a Port or Protocol based VLAN. . . . . . . . . . . . . 2-9
Create a Port or Protocol Based VLAN . . . . . . . . . . . . . 2-9
Adding Ports to a VLAN . . . . . . . . . . . . . . . . . . . . . . . . . 2-9
Configuring VLAN Trunk Ports. . . . . . . . . . . . . . . . . . . . . . 2-10
Configure Bridging for Non-IP/IPX Protocols . . . . . . . . . . . 2-10
Configure Layer-2 Filters . . . . . . . . . . . . . . . . . . . . . . . . . . 2-10
Monitor Bridging. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-11
Configuration Examples. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 2-11
Creating an IP or IPX VLAN. . . . . . . . . . . . . . . . . . . . . . . . 2-11
Chapter 3 IP Routing Configuration Guide
IP Routing Overview. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3-1
IP Routing Protocols. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3-1
Unicast Routing Protocols . . . . . . . . . . . . . . . . . . . . . . . 3-1
Multicast Routing Protocols . . . . . . . . . . . . . . . . . . . . . . 3-2
xii SSR User Refere nce Manual
Page 13
Contents
Configuring IP Interfaces and Parameters . . . . . . . . . . . . . . . . . 3-2
Configure IP Addresses to Ports . . . . . . . . . . . . . . . . . . . . . 3-2
Configure IP Interfaces for a VLAN . . . . . . . . . . . . . . . . . . . 3-3
Specify Ethernet Encapsulation Method. . . . . . . . . . . . . . . . 3-3
Configure Address Resolution Protocol . . . . . . . . . . . . . . . . 3-3
Configure ARP Cache Entries . . . . . . . . . . . . . . . . . . . . 3-4
Configure Proxy ARP . . . . . . . . . . . . . . . . . . . . . . . . . . . 3-4
Configure DNS Parameters . . . . . . . . . . . . . . . . . . . . . . . . .3-4
Configure IP Services (ICMP) . . . . . . . . . . . . . . . . . . . . . . . 3-5
Monitor IP Parameters . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3-5
Configuration Examples . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3-6
Assigning IP/IPX Interfaces . . . . . . . . . . . . . . . . . . . . . . . . . 3-6
Chapter 4 RIP Configuration Guide
RIP Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 4-1
Configure RIP. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 4-1
Enabling and Disabling RIP . . . . . . . . . . . . . . . . . . . . . . . . . 4-1
Configuring RIP Interfaces . . . . . . . . . . . . . . . . . . . . . . . . . . 4-1
Configure RIP Parameters . . . . . . . . . . . . . . . . . . . . . . . . . . 4-2
Configure RIP Route Preference . . . . . . . . . . . . . . . . . . . . . 4-3
Configure RIP Route Default-Metric. . . . . . . . . . . . . . . . . . . 4-3
Monitoring RIP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 4-4
Configuration Example . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 4-5
Chapter 5 OSPF Configuration Guide
OSPF Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-1
Configure OSPF. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-1
Enable OSPF . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . .5-2
Configure OSPF Interface Parameters. . . . . . . . . . . . . . . . . 5-2
Configure an OSPF Area . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-4
SSR User Reference Manual xiii
Page 14
Contents
Configure OSPF Area Parameters. . . . . . . . . . . . . . . . . . . . 5-4
Create Virtual Links . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-5
Configure Autonomous System External (ASE) Link
Advertisements. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-6
Configure OSPF over Non-Broadcast Multiple Access . . . . 5-6
Monitoring OSPF . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5-6
OSPF Configuration Examples . . . . . . . . . . . . . . . . . . . . . . . . . 5-8
Chapter 6 Routing Policy Configuration Guide
Route Import and Export Policy Overview . . . . . . . . . . . . . . . . . 6-1
Preference . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-1
Import Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-2
Import-Source. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-3
Route-Filter. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-4
Export Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-4
Export-Destinatio n . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-4
Export-Source. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-4
Route-Filter. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-5
Specifying a Route Filter . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-5
Aggregates and Generates . . . . . . . . . . . . . . . . . . . . . . . . . 6-6
Aggregate-Destination . . . . . . . . . . . . . . . . . . . . . . . . . . 6-7
Aggregate-Source . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-7
Route-Filter. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-7
Authentication. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-8
Authentication Methods . . . . . . . . . . . . . . . . . . . . . . . . . 6-8
Authentication Keys and Key Management . . . . . . . . . . 6-8
Configure Simple Routing Policies. . . . . . . . . . . . . . . . . . . . . . . 6-9
Redistributing Static Routes. . . . . . . . . . . . . . . . . . . . . . . . . 6-9
Redistributing Directly Attached Networks . . . . . . . . . . . . . 6-10
Redistributing RIP into RIP. . . . . . . . . . . . . . . . . . . . . . . . . 6-10
Redistributing RIP into OSPF. . . . . . . . . . . . . . . . . . . . . . . 6-10
xiv SSR User Re ference Manual
Page 15
Contents
Redistributing OSPF to RIP . . . . . . . . . . . . . . . . . . . . . . . . 6-11
Redistributing Aggregate Routes . . . . . . . . . . . . . . . . . . . . 6-11
Simple Route Redistribution Examples . . . . . . . . . . . . . . . 6-11
Example 1: Redistribution into RIP. . . . . . . . . . . . . . . . 6-11
Example 2: Redistribution into OSPF. . . . . . . . . . . . . . 6-13
Configure Advanced Routing Policies . . . . . . . . . . . . . . . . . . . 6-15
Export Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-15
Creating an Export Destination. . . . . . . . . . . . . . . . . . . . . . 6-16
Creating an Export Source . . . . . . . . . . . . . . . . . . . . . . . . . 6-17
Import Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-17
Creating an Import Source . . . . . . . . . . . . . . . . . . . . . . . . . 6-18
Creating a Route Filter . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6-18
Creating an Aggregate Route. . . . . . . . . . . . . . . . . . . . . . . 6-18
Creating an Aggregate Destination . . . . . . . . . . . . . . . . . . 6-20
Creating an Aggregate Source. . . . . . . . . . . . . . . . . . . . . . 6-20
Examples of Import Policies . . . . . . . . . . . . . . . . . . . . . . . . 6-20
Example 1: Importing from RIP . . . . . . . . . . . . . . . . . . 6-20
Example 2: Importing from OSPF. . . . . . . . . . . . . . . . . 6-23
Examples of Export Policies. . . . . . . . . . . . . . . . . . . . . . . . 6-27
Example 1: Exporting to RIP . . . . . . . . . . . . . . . . . . . . 6-27
Example 2: Exporting to OSPF. . . . . . . . . . . . . . . . . . . 6-31
Chapter 7 Multicast Routing Configuration Guide
IP Multicast Overview. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-1
IGMP Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-1
DVMRP Overview. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-1
Configure IGMP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-2
Configuring IGMP on an IP Interface . . . . . . . . . . . . . . . . . . 7-2
Configure IGMP Query Interval . . . . . . . . . . . . . . . . . . . . . . 7-3
Configure IGMP Response Wait Time . . . . . . . . . . . . . . . . . 7-3
Configure Per-Interfac e Control of IGMP Membership. . . . . 7-3
SSR User Reference Manual xv
Page 16
Contents
Configure DVMRP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-4
Starting and Stopping DVMRP. . . . . . . . . . . . . . . . . . . . . . . 7-4
Configure DVMRP on an Interface. . . . . . . . . . . . . . . . . . . . 7-4
Configure DVMRP Parameters . . . . . . . . . . . . . . . . . . . . . . 7-4
Configure the DVMRP Routing Metric . . . . . . . . . . . . . . . . . 7-5
Configure DVMRP TTL and Scope . . . . . . . . . . . . . . . . . . . 7-5
Configure a DVMRP Tunnel . . . . . . . . . . . . . . . . . . . . . . . . . 7-6
Monitor IGMP and DVMRP . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-7
Configuration Examples. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7-7
Chapter 8 IPX Routing Configuration Guide
IPX Routing Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-1
RIP (Routing Information Protocol) . . . . . . . . . . . . . . . . . . . 8-1
SAP (Service Advertising Protocol) . . . . . . . . . . . . . . . . . . . 8-2
Configuring IPX RIP and SAP . . . . . . . . . . . . . . . . . . . . . . . . . . 8-2
IPX RIP. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-2
IPX SAP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-3
Creating IPX Interfaces . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-3
IPX Addresses . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-3
Configuring IPX Interfaces and Para met e rs. . . . . . . . . . . . . . . . 8-3
Configure IPX Addresses to Ports . . . . . . . . . . . . . . . . . . . . 8-3
Configure IPX Interfaces for a VLAN . . . . . . . . . . . . . . . . . . 8-3
Specify IPX Encapsulation Method . . . . . . . . . . . . . . . . . . . 8-4
Configure IPX Routing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-4
Enable IPX RIP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-4
Enable SAP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-5
Configure Static Routes . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-5
Configure Static SAP Table Entries . . . . . . . . . . . . . . . . . . . 8-5
Control Access to IPX Networks . . . . . . . . . . . . . . . . . . . . . 8-5
Create an IPX Access Control List. . . . . . . . . . . . . . . . . 8-6
Create an IPX SAP Access Control List. . . . . . . . . . . . . 8-6
xvi SSR User Re ference Manual
Page 17
Create an IPX RIP Access Control List . . . . . . . . . . . . . 8-7
Monitor an IPX Network . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-7
Configuration Examples . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8-7
Chapter 9 Security Configuration Guide
Security Overview . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-1
Configuring SSR Access Security . . . . . . . . . . . . . . . . . . . . . . . 9-1
Configure TACACS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-1
Monitor TACACS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-2
Configure Passwords . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-2
L2 Security Filters. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-2
Configuring Layer-2 Address Filters. . . . . . . . . . . . . . . . . . . 9-3
Configuring Layer-2 Port-to-Address Lock Filters . . . . . . . . 9-4
Contents
Configuring Layer-2 Static Entry Filters . . . . . . . . . . . . . . . . 9-4
Configuring Layer-2 Secure Port Filters . . . . . . . . . . . . . . . . 9-5
Monitor Layer-2 Security Filters . . . . . . . . . . . . . . . . . . . . . . 9-5
Layer-2 Filter Examples . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-7
Example 1: Address Filters. . . . . . . . . . . . . . . . . . . . . . . 9-7
Example 2 : Secure Ports. . . . . . . . . . . . . . . . . . . . . . . . 9-8
L3 Access Control Lists (ACLs) . . . . . . . . . . . . . . . . . . . . . . . . . 9-9
Traffic Filters at Layer-3 and 4 (Access Control List) . . . . . . 9-9
The Anatomy of an ACL rule . . . . . . . . . . . . . . . . . . . . . . . . 9-9
The Ordering of ACL rules . . . . . . . . . . . . . . . . . . . . . . . . . 9-10
Implicit Deny Rule. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-11
Applying ACLs to Interfaces . . . . . . . . . . . . . . . . . . . . . . . . 9-12
Applying ACLs to Services . . . . . . . . . . . . . . . . . . . . . . . . . 9-13
ACL Logging. . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-13
Maintaining ACLs offline using TFTP or RCP . . . . . . . . . . 9-14
Maintaining ACLs using the ACL Editor . . . . . . . . . . . . . . . 9-15
Configure ACL . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-15
SSR User Reference Manual xvii
Defining an IP ACL. . . . . . . . . . . . . . . . . . . . . . . . . . . . 9-16
Page 18
Contents
Defining an IPX ACL. . . . . . . . . . . . . . . . . . . . . . . . . . . 9-16
Applying an ACL to an Interface. . . . . . . . . . . . . . . . . . 9-16
Applying an ACL to a Service. . . . . . . . . . . . . . . . . . . . 9-16
Edit an ACL with the ACL Editor. . . . . . . . . . . . . . . . . . 9-16
Monitor Access Control Lists . . . . . . . . . . . . . . . . . . . . . . . 9-16
Chapter 10 QoS Configuration Guide
QoS and L2/L3/L4 flow Overview. . . . . . . . . . . . . . . . . . . . . . . 10-1
Layer-2, 3, 4 Flow Specification . . . . . . . . . . . . . . . . . . . . . 10-1
Precedence for Layer-3 Flows . . . . . . . . . . . . . . . . . . . . . . 10-2
SSR Queuing Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10-2
Configure Layer-2 QoS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10-2
Configure Layer-3 and 4 QoS . . . . . . . . . . . . . . . . . . . . . . . . . 10-3
Configure IP QoS Policies . . . . . . . . . . . . . . . . . . . . . . . . . 10-3
Set an IP QoS Policy . . . . . . . . . . . . . . . . . . . . . . . . . . 10-4
Specify Precedence for an IP QoS Policy . . . . . . . . . . 10-4
Configure IPX QoS Policies . . . . . . . . . . . . . . . . . . . . . . . . 10-4
Set an IPX QoS Policy . . . . . . . . . . . . . . . . . . . . . . . . . 10-4
Specify Precedence for an IPX QoS Policy . . . . . . . . . 10-5
Configure SSR Queuing Policy . . . . . . . . . . . . . . . . . . . . . . . . 10-5
Allocating Bandwidth for a Weighted-Fair Queuing Policy. 10-5
Monitor QoS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10-6
Chapter 11 Performance Monitori ng Guide
Performance Monitoring Overview. . . . . . . . . . . . . . . . . . . . . . 11-1
xviii SSR User Refere nce Manual
Page 19
Chapter 1
Chapter 1 SmartSwitch Router Product
Overview
The 8-slot SmartSwitch Router (SSR-8) provides non-blocking, wire-speed Layer-2
(switching), Layer-3 (routing) and Layer-4 (application) switching. The hardware
provides wire-speed performance regardless of the performance monitoring, filtering,
and Quality of Service (QoS) features enabled by the software. You do not need to
accept performance compromises to run QoS or access control lists (ACLs).
The following table lists the basic hardware and software specifications for the SSR-8.
Feature Specification
Throughput • 16-Gbps non-blocking switching fabric
• 15 million packets-per-second routing throu ghput
Capacity • Up to 250,000 routes
• Up to 2,000,000 Layer-4 application flows
• 400,000 Layer-2 MAC addresses
• 4,096 Virtual LANs (VLANs)
• 20,000 Layer-2 security and access-control filters
• 3MB input/output buffering per Gigabit por t
• 1MB input/output buffering per 10/100 port
Routing protocols • IP: RIPv1/v2, OSPF
• IPX: RIP, SAP
• Multicast: IGMP, DVMRP
Bridging and
VLAN protocols
Media Interface
protocols
• 802.1d Spanning Tree
• 802.1Q (VLAN trunking)
• 802.3 (10Base-T)
• 802.3u (100Base-TX, 100BASE-FX)
• 802.3x (1000Base-SX, 1000Base-LX)
• 802.3z (1000Base-SX, 1000Base-LX)
Page 20
Chapter 1: SmartSwitch Router Product Overview
Feature Specification
Quality of Service
(QoS)
RMON • RMONv1/v2 for each port
Management • SNMP
Port mirroring • Traffic to Control Module
Hot swapping • Power supply (when redundant supply is installed
Redundancy • Redundant and hot-swappable power supplies
• Layer-2 prioritization (802.1p)
• Layer-3 source-destination flows
• Layer-4 source-destination flows
• Layer-4 application flows
• CoreWatch Element Manager (GUI)
• Emacs-like Command Line Interface (CLI)
• Traffic from specific ports
• Traffic to specific chassis slots (line cards)
and online)
Supported Media (Encapsulation Typ e)
The SSR supports the following industry-standard networking media:
• IP: IEEE 802.3 SNAP and Ethernet Type II
• IPX: IEEE 802.3 SNAP, Ethernet Type II, IPX 802.3, 802.2
• 802.1Q VLAN Encapsulation
Supported Routing Protocols
The SSR supports many routing protocols based on open standards. The SSR can
receive and forward packets concurrently from any combination of the following:
• Interior Gateway Protocols
• Open Shortest Path First (OSPF) Version 2
• Routing Information Protocol (RIP) Version 1, 2
1 - 2 SSR User Reference Manual
Page 21
Chapter 1: SmartSwitch Router Product Overview
“IP Routing Configuration Guide” on page 3 - 1 describes these protocols in detail.
The SSR supports the following Novell IPX routing protocols:
• Routing Information Protocol (RIP)
• Service Advertising Protocol (SAP)
“IPX Routing Configuration Guide” on page 8 - 1 describes these protocols in detail.
Configuring the Cabletron SmartSwitc h Router
The SSR provides a command line interface (CLI) that allows you to configure and
manage the SSR. The CLI has several command modes, each of which provides a
group of related co mmands that you can use t o configure the SSR and display its stat us.
Some commands are available to all users; others can be executed only after the user
enters an “Enable” password.
You use the CLI to configure ports, IP/IPX interfaces, routing, switching, security
filters and Quality of Service (QoS) policies.
Understanding the Command Line Interface
The SSR Command Line Interface (CLI) provides access to several different command
modes. Each command mode provides a group of related commands. This chapter
describes how to access and list the commands available in each command mode and
explains the primary uses for each command mode. This chapter also describes the
other features of the user interface.
SSR commands can be entered at a terminal connected to the access server or router
using the command line interface (CLI). The SSR can also be configured using the
CoreW atch Java-based management application. Using CoreWatch is described in the
CoreWatch User’s Guide.
Basic Line Editing Commands
The CLI supports EMACs-like line editing commands. The following table lists some
commonly used commands.
Key sequence Command
Ctrl-A Move cursor to beginning of line
Ctrl-B Move cursor back one character
SSR User Reference Manual 1 - 3
Ctrl-D Delete character
Page 22
Chapter 1: SmartSwitch Router Product Overview
Key sequence Command
Ctrl-E Move cursor to end of line
Ctrl-F Move cursor forward one character
Ctrl-N Scroll to next command in command
history (use the
command to di splay the history)
Ctrl-P Scroll to previous command in com-
mand history
Ctrl-U Erase entire line
Ctrl-X Erase from cursor to end of line
Ctrl-Z Exit current access mode to previous
access mode
cli show history
Access Modes
The SSR CLI has four access modes.
• User – Allows you to display basic information and use basic utilities such as ping
but does not allow you to display SNMP, filter and access control list information or
make other configuration changes. You are in User mode when the command
prompt ends with this character:
>
• Enable – Allows you to display SNMP, filter, and access control information as well
as all the information you can display in User mode. To enter Enable mode, enter the
enable
Enable mode, the command prompt ends with this character:
#
• Configure – Allows you to make configuration changes. To ent er Configure mode,
first enter Enable mode (
from the Enable command prompt. When you are in Configur e mode, the command
prompt ends with these characters:
(config)#
• Boot – This mode appears when the SSR the extern al flash card or the system image
is not found d uring boot up. You should ent er the reboot command to reset the SSR.
If the SSR still fails to bootup, please call Cabletron Technical Support.
command, then supply the password when prompted. When you are in
enable
command), then enter the
configure
command
1 - 4 SSR User Reference Manual
Page 23
Chapter 1: SmartSwitch Router Product Overview
Note:
When you are in Conf igure or Enable mode, use the
exit to the previous access mode.
Note:
User Mode
After you log in to the SSR, you are automatically in User mode. The User commands
available are a subset of those available in Enable mode. In general, the User
commands allow you to display basic information and use basic utilities such as ping
information.
To list the User commands, enter:
List the User commands.
The command prompt will show the name of the SmartSwitch Router in
front of the mode character(s). The default name is “ssr”.
exit
command or press Ctrl-z to
When you exit Configure mode, the CLI will ask you whether you want to
activate the configuration commands you have issued. If yo u enter
Y
(Y es ),
the configuration commands you issued are placed into effect and the
SmartSwitch Router’s configuration is changed accordingly. However, the
changes are not written to the Startup configuration f ile in the Control Module’s boot flash and therefore are not reinstated after a reboot.
?
The User mode command prompt consists of the SSR name followed by the angle
bracket (>):
ssr>
The default name is SSR unless it has been changed during initial configuration using
the system set name command. Refer to the SmartSwitch Router Command Line
Interface Reference Manual for information on the system facility.
To list the commands available in User mode, enter a question mark (?) as shown in
the following example:
ssr> ?
aging - Show L2 and L3 Aging information
cli - Modify the command line interface behavior
dvmrp - Show DVMRP related parameters
enable - Enable privileged user mode
exit - Exit current mode
file - File manipulation commands
igmp - Show IGMP related parameters
ipx - Show IPX related parameters
SSR User Reference Manual 1 - 5
Page 24
Chapter 1: SmartSwitch Router Product Overview
l2-tables - Show L2 Tables information
logout - Log off the system
multicast - Configure Multicast related parameters
ping - Ping utility
statistics - Show or clear SSR statistics
stp - Show STP status
traceroute - Traceroute utility
vlan - Show VLAN-related parameters
Enable Mode
Enable mode provides more facilities than User mode. Y ou can display critical features
within Enable mode including router configuration, access control lists and SNMP
statistics. To enter Enable mode, enter the
password when prompted.
To list the Enable commands, enter:
enable
command, then supply the
List the user Enable commands.
The Enable mode command prompt consi sts of the S SR name fo llo wed by th e pound
sign(#):
ssr#
T o list the commands available in Enable mode, enter a question mark (?) as shown in
the following example:
ssr# ?
acl - Show L3 Access Control List
aging - Show L2 and L3 Aging information
arp - Show or modify ARP entries
cli - Modify the command line interface
configure - Enter Configuration Mode
copy - Copy configuration database
dvmrp - Show DVMRP related parameters
enable - Enable privileged user mode
exit - Exit current mode
file - File manipulation commands
filters - Show L2 security filters
http - Show http parameters
igmp - Show IGMP related parameters
interface - Show interface related parameters
ip - Show IP related parameters
ip-router - Show unicast IP Routing related
?
behavior
parameters
1 - 6 SSR User Reference Manual
Page 25
Chapter 1: SmartSwitch Router Product Overview
ipx - Show IPX related parameters
l2-tables - Show L2 Tables information
logout - Log off the system
mtrace - Multicast Traceroute utility
multicast - Configure Multicast related parameters
ospf - Show/Monitor Open Shortest Path First
Protocol (OSPF).
ping - Ping utility
port - Show or change Port parameters
qos - Show Quality of Service parameters
reboot - Reboot the system
rip - Show/Query Routing Information Protocol
(RIP) tables
snmp - Show SNMP related parameters.
statistics - Show or clear SSR statistics
stp - Show STP status
system - Show system-wide parameters
tacacs - Show TACACS related parameters
traceroute - Traceroute utility
vlan - Show VLAN-related parameters
To exit Enable mode and return to User mode, use one of the following commands:
Exit Enable mode.
Configure Mode
Configure mode provides the capabilities to configure all features and functions on the
SSR. You can configure features and functions within Configure mode including
router configuration, access control lists and spanning tree.
To list the Configure commands, enter:
List the Configure commands.
The Configure mode command prompt consists of the SSR name followed by the
pound sign (#):
ssr(config)#
T o list the commands availabl e in Configure mode, enter a question mark (?) as shown
in the following example:
ssr(config)# ?
acl - Configure L3 Access Control List
acl-edit - Edit an ACL in the ACL Editor
aging - Configure L2 and L3 Aging
arp - Configure ARP entries
exit
Ctrl-Z
?
SSR User Reference Manual 1 - 7
Page 26
Chapter 1: SmartSwitch Router Product Overview
bgp - Configure Border Gateway Protocol (BGP)
cli - Modify the command line interface behavior
dvmrp - Configure DVMRP related parameters
exit - Exit current mode
filters - Configure L2 security filters
http - Configure SNMP related parameters.
igmp - Configure IGMP related parameters
interface - Configure interface related parameters
ip - Configure IP related parameters
ip-router - Configure Unicast Routing Protocol related
parameters
ipx - Configure IPX related parameters
ospf - Configure Open Shortest Path Protocol (OSPF)
port - Configure Port parameters
qos - Configure Quality of Service parameters
rip - Configure Routing Information Protocol (RIP)
snmp - Configure SNMP related parameters.
stp - Configure STP parameters
system - Configure system-wide parameters
tacacs - Configure TACACS related parameters
vlan - Configure VLAN-related parameters
Special configuration mode commands:
erase - Erase configuration information
negate - Negate a command or a group of commands
no - Negate matching commands
save - Save configuration information
search - Look up a command in configuration
show - Show configuration commands
To exit Configure mode and return to Enable mode, use one of the following
commands:
Exit Configure mode.
Boot PROM Mode
If your SSR does not find a valid system image on the external PCMCIA flash, the
system might enter pro grammable read-only memory (PROM) mode. You should then
reboot the SSR at the boot PROM to restart the system. If the system fails to reboot
successfully, please call Cabletron Systems T ec hnical Supp ort to resolve the prob lem.
To reboot the SSR from the ROM monitor mode, enter the following command.
using line numbers
exit
Ctrl-Z
Reboot in Boot PROM mode.
1 - 8 SSR User Reference Manual
reboot
Page 27
Chapter 1: SmartSwitch Router Product Overview
Disabling a Function or Feature
The CLI provides for an implicit negate. This allows for the “disabling” of a feature or
function which has been “enabled”. Use the
active configuration to “disable” a feature or function which has been enabled. For
example, Spanning Tree Protocol is disabled by default. If after enabling Spanning
Tree Protocol on the SmartSwitch Router, you want to disable STP, you must specify
negate
the
enable
command on the line of the active configuration containing the
command.
negate
command on a specific line of the
Loading System Images and Configuration Files
The SSR contains an internal flash on the Control Module and an external PC flash.
The internal flash contains the SSR boot image and user defined configuration files.
An external PC flash contains the system image executed by the Control module.
When an SSR boots, the boot image is executed first, followed by the system image
and finishing with a configuration file.
stp
Boot and System Image
Only one boot image exists on the internal flash of the SSR Control Module. Multiple
system images can be stored on the external PC flash.
Configuration Files
The SSR uses three special configuration files:
• Active – The commands from the Startup configuration file and any
configuration commands that you have made active from the scratchpad (see
below).
Caution
: The active configuration remains in effect only during the current power
cycle. If you power down or reboot the SSR without saving the active
configuration changes to the Startu p configuration file, the changes are lost.
• Startup – The configuration file that the SSR uses to configure itself when the
system is powered on.
• Scratchpad – The configuration commands you have entered during a
management session. These commands do not become active until you
explicitly activate them. Because some commands depend on other commands
for successful execution, the SSR scratchpad simplifies system configuration by
allowing you to enter configuration commands in any order, even when
dependencies exist. When you activate the commands in the scratchpad, the
SSR sorts out the dependencies and executes the command in the proper
SSR User Reference Manual 1 - 9
Page 28
Chapter 1: SmartSwitch Router Product Overview
sequence.
Loading System Image Software
By default, the SSR boots using the system im age software installed on the Control
Module’s PCMCIA flash card. To upgrade the system software and boot using the
upgraded image, use the following procedure.
1. Display the current boot settings by entering the following command:
system show version
Here is an example:
ctron-ssr-1# system show version
Software Information
Software Version : 1.0
Copyright : Copyright (c) 1996-1998 Cabletron Systems, Inc.
Image Information : Version 1.0, built on Fri Mar 20 19:28:49 1998
Image Boot Location: file:/pc-flash/boot/ssr8/
Note:
In this example, the location “pc-flash” indicates that the SSR is set to use
the factory-installed software on the flash card.
2. Copy the software upgrade you want to install onto a TFTP server that the SSR
can access. (Use the
ping
command to verify that the SSR can reach the TFTP
server.)
3. Enter the following command to copy the software upgrade onto the PCMCIA
flash card in the Control Module:
system image add
<IPaddr-of-TFTP-host> <image-file-name>
Here is an example:
ctron-ssr-1# system image add 10.50.11.12 ssr8000
Downloading image 'ssr8000' from host '10.50.11.12'
to local image ssr8000 (takes about 3 minutes)
kernel: 100%
Image checksum validated.
Image added.
4. Enter the following command to list the images on the PCMCIA flash card and
verify that the new image is on the card:
system image list
Here is an example:
1 - 10 SSR User Reference Manual
Page 29
Chapter 1: SmartSwitch Router Product Overview
ctron-ssr-1# system image list
Images currently available:
ssr8-1.0
5. Enter the following command to select the image file the SSR wi ll use the next
time you reboot the switch.
system image choose
Here is an example:
ctron-ssr-1# system image choose ssr8000_10A9
Making image ssr8-1.0 the active image for next reboot
6. Enter the
Note:
You do not need to activate this change.
system image list
Loading Boot PROM Software
The SSR boots using the boot PROM software in stalled on the Control Module’s
internal memory. To upgrade the boot PROM software and boot using the upgraded
image, use the following procedure.
1. Display the current boot settings by entering the following command:
system show version
Here is an example:
ctron-ssr-1# system show version
Software Information
Software Information
Software Version : 1.0
Copyright : Copyright (c) 1996-1998 Cabletron Systems, Inc.
Image Information : Version 1.0.B.13, built on Wed Mar 25 22:49:07
1998
Image Boot Location: file:/pc-flash/boot/ssr8/
Boot Prom Version : prom-1.0
<file-name>
command to verify the change.
Note:
In this example, the location “pc-flash” indicates that the SSR is set to use
the factory-installed software on the flash card.
2. Copy the software upgrade you want to install onto a TFTP server that the SSR
can access. (Use the
SSR User Reference Manual 1 - 11
ping
command to verify that the SSR can reach the TFTP
Page 30
Chapter 1: SmartSwitch Router Product Overview
server.)
3. Enter the following command to copy the boot PROM upgrade onto the internal
memory in the Control Module:
system promimage upgrade
name>
<IPaddr-of-TFTP-host> <image-file-
Here is an example:
ctron-ssr-1# system promimage upgrade 10.50.11.12 prom2
Downloading image 'prom2' from host '10.50.11.12'
to local image prom2 (takes about 3 minutes)
kernel: 100%
Image checksum validated.
Image added.
4. Enter the following command to verify that the new boot PROM software is on
the internal memory of the Control Module:
system show version
Activate the Configuration Commands in the Scratchpad
The configuration commands you have en tered u sing procedures in this ch apter are in
the Scratchpad but have not yet been activated. Use the following procedure to activate
the configuration commands in the scratchpad.
1. If you have not alread y done so, enter the
in the CLI.
enable
command to enter Enable mode
2. If you have not already done so, enter the
configure
command to enter
Configure mode in the CLI.
3. Enter the following command:
save active
The CLI displays the following message:
Do you want to make the changes Active? [y]
4. Enter
Note:
yes
to activate the changes.
If you exit Config ure mode (by ent ering the exit comm and or pressi ng Ctrlz), the CLI will ask you whether you want to make the changes in the
scratchpad active.
1 - 12 SSR User Reference Manual
Page 31
Chapter 1: SmartSwitch Router Product Overview
Copy the Configuration to the Startup Configuration File
After you save the configuration commands in the scratchp ad, the Control Module
executes the commands and makes the corresponding configuration changes to the
SSR. However, if you power down or reboot the SSR, the new changes are lost. Use
the following procedure to save the changes into the Startup configuration file so that
the SSR reinstates the changes when you reboot the software.
1. If you have not alread y done so, enter the
in the CLI.
2. Enter the following command to copy the configur ation changes in the Active
configuration to the Startup configuration:
copy active to startup
3. When the CLI displays the following message, enter
Are you sure you want to overwrite the Startup configurat ion? [n]
Note:
You also can save active changes to the Startup configuration file from
within Configure mode by entering the following com mand:
save startup
The new configuration changes are added to the Startup configuration file stored in the
Control Module’s boot flash.
Managing the SSR
The SSR contains numerous system facilities for system management. You can
perform configuration management tasks on the SSR including:
enable
command to enter Enable mode
yes
to save the changes.
• Setting the SSR name
• Setting the SSR date and time
• Configuring the CLI
• Configuring SNMP services
SSR User Reference Manual 1 - 13
Page 32
Chapter 1: SmartSwitch Router Product Overview
Set SSR Name
The SSR name is set to ssr by default. You may customize the name for the SSR by
performing the following in Configure mode:.
Set the SSR name.
Set SSR Date and Time
The SSR system time keeps track of time as entered by the user. No time coordination
is maintained between the SSR and a source for Universal T ime. To configure the SSR
date and time, enter the following command in Enable mode:
Set SSR date and time.
Configure the SSR CLI
You can customize the CLI display format to a desired line length or row count. To
configure the CLI terminal display, enter the following command in Enable mode:
Configure the CLI terminal display .
Configure SNMP Services
system set name
system set date year
<day>
day
second
cli set terminal rows
<sec>
<system-name>
<year>
hour
<hour>
min
<num>
month
<month>
<min>
columns
<num>
The SSR accepts SNMP sets and gets from an SNMP manag er . Y ou can configure SSR
SNMP parameters including community strings and trap server target addresses.
To configure the SSR SNMP community string, enter the following command in
Configure mode:
Configure the SNMP community
string.
snmp set community
privilege read|read-write
<community-name>
To configure the SNMP trap server target address, enter the following command in
Configure mode:
Configure the SNMP trap server target
address.
snmp set target
nity-name>
<IP-addr>
[status enable|disable]
community
<commu-
1 - 14 SSR User Reference Manual
Page 33
Configure DNS
The SSR allows you to configure up to three Domain Name Service (DNS) servers.
To configure the DNS, the following command in Configure mode.
Chapter 1: SmartSwitch Router Product Overview
Configure DNS.
Configure HTTP Services
The SSR contains an HTTP server for responding to access from CoreW atch. You have
the ability to stop the HTTP server or disable authentication.
T o configure the HTTP par ameters, enter one of the followin g commands in Configure
mode:
Stop the HTTP server.
Stop HTTP authentication.
Monitoring Configuration
The SSR provides many commands for displaying configuration information. After
you add configuration items and commit them to the active configuration, you can
display them using the following commands.
system set dns server
<IPaddr>[,<IPaddr>[,<IPaddr>
<name>
http stop
http disable authentication
]] domain
Display history buffer.
Show terminal settings.
Show accesses to the HTTP server.
Show all HTTP related information.
Show HTTP server status.
Show HTTP server related statistics.
Show all accesses to the SNMP agent.
Show all SNMP information.
SSR User Reference Manual 1 - 15
cli show history
cli show terminal
http show access
http show all
http show server
http show statistics
snmp show access
snmp show all
Page 34
Chapter 1: SmartSwitch Router Product Overview
Show chassis ID.
Show the SNMP community strings.
Show SNMP related statistics.
Show trap target related configuration.
Show the active configuration of the
system.
Show the contents of the boot log file,
which contains all the system messages
generated during boot u p.
Show the most recent Syslog messages
kept in the local syslog message buffer.
Show the contact information (administrator name, phone number, and so on).
Show the SSR date and time.
Show the IP addresses and domain
names for DNS servers.
snmp show chassis-id
snmp show community
snmp show statistics
snmp show trap
system show active-config
system show bootlog
system show syslog buffer
system show contact
system show date
system show dns
Show SSR hardware information.
Show SSR location.
Show SSR name.
Show the type of Power-On Self Test
system show hardware
system show location
system show name
system show poweron-selftest-mode
(POST) that should be performed.
Show the configuration changes in the
system show scratchpad
scratchpad. These changes have not yet
been activated.
Show the startup configuration for the
system show startup-config
next reboot.
Show the IP address of the SYSLOG
system show syslog
server and the level of messages the
SSR sends to the server.
1 - 16 SSR User Reference Manual
Page 35
Chapter 1: SmartSwitch Router Product Overview
Lists the last five Telnet connections to
the SSR.
Show the default terminal settings
(number of rows, number of columns,
and baud rate.
Show SSR uptime.
Show the software version running on
the SSR.
system show telnet-access
system show terminal
system show uptime
system show version
SSR User Reference Manual 1 - 17
Page 36
Chapter 1: SmartSwitch Router Product Overview
1 - 18 SSR User Reference Manual
Page 37
Chapter 2
)
)
Chapter 2 Bridging Configuration Guide
Bridging Overview
The SmartSwitch Router provides the following bridging functions:
• Complies with the IEEE 802.1d standard
• Complies with the IGMP multicast bridging stan dard
• Provides wire-speed address-based bridging or flow-based bridging
• Provides the ability to logically segment a transparently bridged network into virtual
local-area networks (VLANs) based on physical ports or protocol (IP or IPX or
bridged protocols like Appletalk)
• Allows frame filtering based on MAC address for bridged and multicast traffic
• Provides integrated routing and bridging, which supports bridging of intra-VLAN
traffic and routing of inter-VLAN traffic
Spanning Tree (IEEE 802.1d
Spanning tree (IEEE 802.1d) allows bridges to dynamically discover a subset of the
topology that is loop-free. In addition, the loop-free tree that is discovered contains
paths to every LAN segment.
Bridging Modes (Flow-Based and Address-Based
The SSR provides the following types of wire-speed bridging:
Address-based bridging - The SSR performs this type of bri d gi ng by looking up the
destination address in an L2 lookup table on the line card that receives the bridge
packet from the network. The L2 lookup table indicates the exit port(s) for the bridged
packet. If the packet is addressed to the SSR's own MAC add ress, the packet is rou ted
rather than bridged.
Flow-based bridging - The SSR performs this type of bridging by looking u p an entry
in the L2 lookup table containing both the source and destination addresses of the
received packet in order to determine how the packet is to be handled.
The SSR ports perform address-based bridging by default but can be configured to
perform flow-based bridging instead, on a per-port basis . A port cannot be configured
to perform both types of bridging at the same time.
The SSR performance is equivalent when perform ing flow-based bridgin g or address based bridging. However , add ress-based bridging is more eff icient because it requires
Page 38
Chapter 2: Bridging Configuration Guide
fewer table entries while flow-based bridging provides tighter management a nd
control over bridged traffic.
VLAN Overview
V irtual LANs (VLANs) are a means of dividing a physical network into seve ral logical
(virtual) LANs. The division can be done on the basis of various criteria, giving rise
to different types of VLANs. For example, the simplest type of VLANs is the portbased VLAN. Port-based VLANs divide a network into a number of VLANs by
assigning a VLAN to each port of a switching device. Then, any traffic received on a
given port of a switch belongs to the VLAN associated with that port.
The primary use of VLANs is for broadcast containment. A layer-2 (L2) broadcast
frame is normally transmitted all over a bridged network. By dividing the network into
VLANs, the range of a broadcast is limited, i.e., the broadcast frame is transmitted
only to the VLAN to which it belongs. This reduces the broadcast traffic on a network
by an appreciable factor.
The type of VLAN depends upon one criterion: how a received frame is classified as
belonging to a particular VLAN. VLANs can be categorized into the following types:
1. Port based
2. MAC address based
3. Protocol based
4. Subnet based
5. Multicast based
6. Policy based
Detailed information about these types of VLANs is beyond t he scope of this manual.
Each type of VLAN is briefly explained in the following subsections.
Port-based VLANs
Ports of L2 devices (switches, bridges) are assigned to VLANs. Any traffic received
by a port is classified as belonging to the VLAN to which the port belongs. For
example, if ports 1, 2, and 3 belong to the VLAN nam ed “Marketing”, then a broadcast
frame received by port 1 is transmitted on ports 2 and 3. It is not transmitted on any
other port .
MAC-address-based VLANs
In this type of VLAN, each switch (or a central VLAN information server) keeps track
of all MAC addresses in a network and maps them to VLANs, based on information
2 - 2 SSR User Reference Manual
Page 39
Chapter 2: Bridging Configuration Guide
configured by the network administrator. When a frame is received at a port, its
destination MAC address is looked up in the VLAN database, which returns the VLAN
to which this frame belongs.
This type of VLAN is p owerf ul in t he s ens e that net wor k devices such as printe r s and
workstations can be moved anywhere in the network without the need for network
reconfiguration. However , the administration is intensive because all MAC addresses
on the network need to be known and configured.
Protocol-based VLANs
Protocol-based VLANs divide the physical network into logical VLANs based on
protocol. When a frame is received at a port, its VLAN is determined by the protocol
of the packet. For example, there cou ld be separate VLANs for IP, IPX and Appletalk.
An IP broadcast frame will only be sent to all ports in the IP VLAN.
Subnet-based VLANs
Subnet-based VLANs are a subset of protocol based VLANs and determine the VLAN
of a frame based on the subnet to which the frame belongs. T o do this, the switch must
look into the network layer header of the incoming frame. This type of VLAN behaves
similar to a router by segregating different subnets into different broadcast domains.
Multicast-based VLANs
Multicast-based VLANs are created dynamically for multicast groups. T y pically , each
multicast group corresponds to a different VLAN. This ensures that multicast frames
are received only by those ports that are connected to members of the appropriate
multicast group.
Policy-based VLANs
Policy-based VLANs are the most general definition of VLANs. Each incoming
(untagged) frame is looked up in a policy database , which determines the VLAN to
which the frame belongs. For example, you could set up a policy which creates a
special VLAN for all email traffic between the management of fi cers of a co mpany, so
that this traffic will not be seen anywhere else.
SSR VLAN Support
The SSR supports:
• Port-based VLANs
• Protocol-based VLANs
• Subnet-based VLANs
When using the SSR as an L2 bridge/switch, use the port-based and protocol-based
VLAN types. When using the SSR as a combined switch and router, use the subnetbased VLANs in addition to port-based an d protocol-based VLANs. It is not necessary
SSR User Reference Manual 2 - 3
Page 40
Chapter 2: Bridging Configuration Guide
to remember the types of VLANs in order to configure the SSR, as seen in the section
on configurin g the SSR.
VLANs and the SSR
VLANs are an integral part of the SSR family of switching routers. The SSR switching
routers can function as layer-2 (L2) switches as well as fully-functonal layer-3 (L3)
routers. Hence they can be viewed as a switch and a router in one box. To provide
maximum performance and functionality , the L2 and L3 aspects of the SSR switching
routers are tightly coupled.
The SSR can be used purely as an L2 switch. Fram es arrivin g at any p ort are b ridged
and not routed. In this case, setting up VLANs and associating ports with VLANs is
all that is required. You can set up the SSR switching router t o use port-based VLANs,
protocol-based VLANs, or a mixture of the two types.
The SSR can also be used purely as a router, i.e., each physical port of the SSR is a
separate routing interface. Packets received at any interface are routed and not bridged.
In this case, no VLAN configuration is required. Note that VLANs are still created
implicitly by the SSR as a result of creating L3 interfaces for IP and/or IPX. However,
these implicit VLANs do not need to be created or configured manually . The implicit
VLANs created by the SSR are subnet-based VLANs.
Most commonly , an SSR is used as a combined switch and router . For example, it may
be connected to t w o su bnet s S1 and S2. Port s 1-8 belong to S1 and ports 9-16 b elo ng
to S2. The required behavior of the SSR is that intra-subnet frames be brid ged and
inter-subnet packets be routed. In other words, traffic between two workstations that
belong to t he same subnet should be bridged, and traffic be tween two work stations that
belong to different subnets should be routed.
The SSR switching routers use VLANs to achieve this behavior. This means that a L3
subnet (i.e., an IP or IPX subnet) is mapped to a VLAN. A given subnet maps to
exactly one and only one VLAN. With this definition, the terms VLAN and subnet are
almost interchangeable.
To configure an SSR as a combined switch and router, the administrator must create
VLANs whenever multiple ports of the SSR are to belong to a particular VLAN/
subnet. Then the VLAN must be bound to an L3 (IP/IPX) interface so that the SSR
knows which VLAN maps to which IP/IPX subnet.
Ports, VLANs, and L3 Interfaces
The term port refers to a physical conn ector on the SSR, such as an ethernet port. Each
port must belong to at least one VLAN. When the SSR is unconfigured, each port
belongs to a VLAN called the “default VLAN”. By creating VLANs and adding ports
to the created VLANs, the ports are moved from the default VLAN to the newly
created VLANs.
2 - 4 SSR User Reference Manual
Page 41
Unlike traditional routers, the SSR has the concept of logical interfaces rather than
physical interfaces. An L3 interface is a logical entity created by the administrator . It
can contain more than one physical port. When an L3 interface contains exactly one
physical port, it is equivalent to an interface on a traditional router. When an L3
interface contains several ports, it is equivalent to an interface of a traditional router
which is connected to a layer-2 device such as a switch or bridge.
Access Ports and Trunk Ports (802.1Q support)
The ports of an SSR can be classified into two types, based on VLAN functionality:
access ports and trunk ports. By default, a port is an access port. An access port can
belong to at mos t one VLAN of the foll owing types: IP, IPX or bridged pr otocols. The
SSR can automatically determine whether a received frame is an IP frame, an IPX
frame or neither. Based on this, it selects a VLAN for the frame. Frames transmitted
out of an access port are untagged, meaning that they contain no special information
about the VLAN to which they belong. Untagged frames are classified as belonging
to a particular VLAN based on the protocol of the frame and the VLAN configured on
the receiving port for that protocol.
For example, if port 1 belongs to VLAN IPX_VLAN for IPX, VLAN IP_VLAN for IP
and VLAN OTHER_VLAN for any other protocol, then an IP frame received b y port 1
is classified as belonging to VLAN IP_VLAN.
Chapter 2: Bridging Configuration Guide
Trunk ports ( 802.1Q) are usually used to connect one VLAN-aware switch to another.
They carry traffic belonging to several VLANs. For example, suppose that SSR A and
B are both configured with VLANs V1 and V2.
Then a frame arrivi ng at a port on SSR A mus t b e s ent t o SSR B, if t he frame bel on gs
to VLAN V1 or to VLAN V2. Thus the por ts on SSR A and B which connect the two
SSRs together must belong to both VLAN V1 and VLAN V2. Also, when these ports
receive a frame, they must be ab le to determ ine whether the frame belongs to V1 or to
V2. This is accomplished by “tagging” the frames, i.e., by prepending information to
the frame in order to identify the VLAN to which the frame belongs. In the SSR
switching routers, trunk ports always transmit and receive tagged frames only. The
format of the tag is specified by the IEEE 802.1Q standard. The only exception to this
is Spanning Tree Protocol frames, which are transmitted as untagged frames.
Explicit and Implicit VLANs
As mentioned earlier, VLANs can either be created explicitly by the administrator
(explicit VLANs) or are created implicitly by the SSR when L3 interfaces are created
(implicit VLANs).
SSR User Reference Manual 2 - 5
Page 42
Chapter 2: Bridging Configuration Guide
Configuring SSR Bridging Functions
Configure Address-based or Flow-based Bridging
The SSR ports perform address- based bridging by default but can be configured to
perform flow-based bri dging inst ead of address -based bridgi ng, on a per-p ort basis. A
port cannot be configured to perform both types of bridging at the same time.
The SSR performance is equivalent when perform ing flow-based bridgin g or address based bridging. However , add ress-based bridging is more eff icient because it req uires
fewer table entries while flow-based bridging provides tighter management a nd
control over bridged traffic.
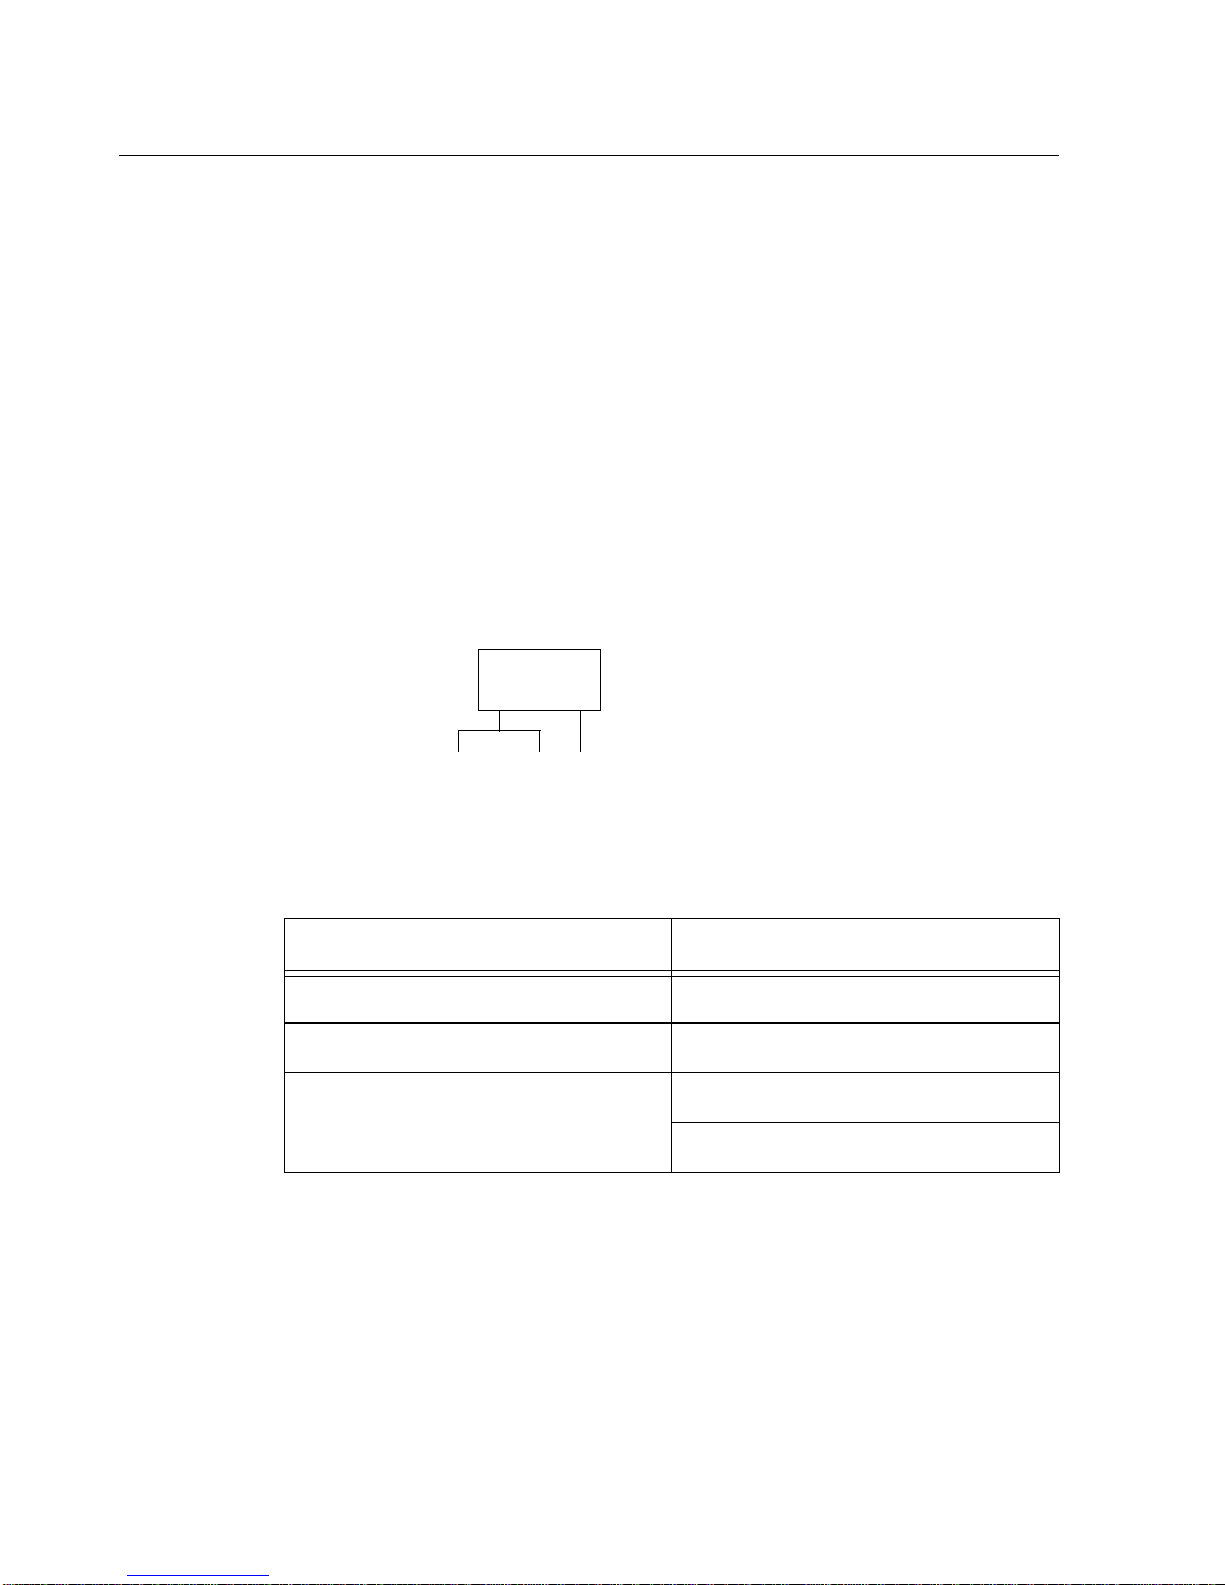
For example, the following illustration shows an SSR with traffic being sent from port
A to port B, port B to port A, port B to port C, and port A to port C.
SSR
ABC
The corresponding b ridge tables f or address-ba sed and flow-bas ed bridging are shown
below. As shown, the bridge table contains more information on the traffic patterns
when flow-based bridging enabled compared to address-based bridging.
Address-Based Bridge Table Flow-Based Bridge Table
A (source)
B (source)
C (destination)
With the SS R configured in flo w-based bridgi ng mode, the netwo rk manager has “per
flow” control of layer-2 traffic. The network manager can then apply Quality of
Service (QoS) policies or security filters based layer-2 traffic flows.
A
B
B
A
→
→
→
→
B
A
C
C
2 - 6 SSR User Reference Manual
Page 43
Chapter 2: Bridging Configuration Guide
To enable a port to flow-based bridging, enter the following command in Configure
Mode.
Configure a port for flow-based bridging.
To change a port from flow-based bridging to address-based bridging, enter the
following command in Configure mode:
Change a port from flow-based bridging to address-based bridging.
Configuring Spanning Tree
The SSR supports only one spanning tree process per SSR. By default, spanning tree
is disabled on the SSR. T o enable spanning tree on the SSR, you perf orm the following
task on the ports where you want spanning tree enabled.
Note:
Enable spanning tree on one or more
ports.
If you are running spanning tree o n o ne or m ore VL ANs, you must en able
spanning tree on all ports belonging to each VLAN.
port flow-bridging
negate
<line-number of active config
containing command>
<port-list>
ing
stp enable port
<port-list>
<port-list>
: port flow-bridg-
|all-ports
|all-ports
Adjust Spanning-Tree Parameters
You may need to adjust certain spanning-tree parameters if the default values are not
suitable for your bridge configuration. Parameters affecting the entire spanning tree ar e
configured with variations of the bridge global configuration command. Interfacespecific parameters are configured with variations of the bridge-group interface
configuration command.
You can adjust spanning-tree parameters by performing any of the tasks in the
following sections:
• Set the Bridge Priority
• Set an Interface Priority
Note:
SSR User Reference Manual 2 - 7
Only network administrat ors with a good understanding of ho w bridges and
the Spanning-Tree Protocol work sh ould make adj us tm ent s to spann i ngtree parameters. Poorly chosen adjustments to these parameters can have a
negative impact on performance. A good source on bridging is the IEEE
802.1d specification.
Page 44
Chapter 2: Bridging Configuration Guide
Set the Bridge Priority
You can globally configure the priority of an individual bridge when two bridges tie
for position as the root bridge, or you can confi gure the likelih ood that a bridge will be
selected as the root bridge. The lower the bridge's priority, the more likely the bridge
will be selected as the root bridge. This priority is determined by default; however, you
can change it.
To set the bridge priority, enter the following command in Configure mode:
Set the bridge priority.
Set a Port Priority
You can set a priority for an interface. When two bridges tie for position as the root
bridge, you configure an interface priority to break the tie. The bridge with the lowest
interface value is elected.
To set an interface priority, enter the following command in Configure mode:
Establish a priority for a specified interface.
Assign Port Costs
Each interface has a port cost associated with it. By convention, the port cost is 1000/
data rate of the attached LAN, in Mbps. You can set different port costs.
To assign port costs, enter the following command in Configure mode:
Set a different port cost other than the
defaults.
stp set bridging priority
stp set port
stp set port
<port-list>
<port-list>
<num>
priority
port-cost
<num>
<num>
Adjust Bridge Protocol Data Unit (BPDU) Intervals
You can adjust BPDU intervals as described in the following sections:
• Adjust the Interval between Hello BPDUs
• Define the Forward Delay Interval
• Define the Maximum Idle Interval
Adjust the Interval between Hello Times
You can specify the interval between hello time.
To adjust this interval, enter the following command in Configure mode:
Specify the interval between hello time
2 - 8 SSR User Reference Manual
stp set bridging hello-time
<num>
Page 45
Define the Forward Delay Interval
The forward delay interval is the amount of time spent listenin g for top ology change
information after an interface has been activated for bridging and before forwarding
actually begins.
To change the default interval setting, enter the following command in Configure
mode:
Chapter 2: Bridging Configuration Guide
Set the default of the forward delay
stp set bridging forward-delay
interval.
Define the Maximum Age
If a bridge does not hear BPDUs from the root bridge within a specified interval, it
assumes that the network has changed and recomputes the spanning-tree topology.
To change the default interval setting, enter the following command in Configure
mode:
Change the amount of time a bridge
stp set bridging max-age
will wait to hear BPDUs from the root
bridge.
Configuring a Port or Protocol based VLAN
T o create a port or prot ocol based VLAN, perform th e following steps in th e Configure
mode.
1. Create a port or protocol based VLAN
2. Add physical ports to a VLAN
<num>
<num>
Create a Port or Protocol Based VLAN
To create a VLAN, perform the following command in the Configure mode.
Create a VLAN.
Adding Ports to a VLAN
To add ports to a VLAN, perform the following command in the Configure mode.
Add ports to a VLAN.
SSR User Reference Manual 2 - 9
vlan create
vlan add ports
<vlan-name> <type>
<port-list>
id
<vlan-name>
to
<num>
Page 46
Chapter 2: Bridging Configuration Guide
Configuring VLAN Trunk Ports
The SSR supports standards-based VLAN trunking between multiple SSRs as defined
by IEEE 802.1Q. 802.1Q add s a head er to a standard Ethernet f rame which includes a
unique VLAN id per trunk between two SSRs. These VLAN ids extend the VLAN
broadcast domain to more than one SSR.
To configure a VLAN trunk, perform the following command in the Configure mode.
Configure 802.1Q VLAN trunks.
vlan make
<port-type> <port-list>
Configure Bridging for Non-IP/IPX Protocols
By default, all non-rout able protocols (AppleTalk and DECnet) are bridged within the
SSR. All physical ports containing non-routable protocols should be assigned to the
same VLAN, thus allowin g bridg ing between po rts. Ro uting can s till b e performed o n
the defined VLAN by assigning an IP or IPX interface.
Configure Layer-2 Filters
Layer-2 security filters on the SSR allow you to configure ports to filter specific MAC
addresses. When defining a Layer-2 security filter, you specify to which ports you
want the filter to apply. Refer to the “Security Configuration Chapter” for details on
configuring Layer-2 filters. You can specify the following security filters:
•Address filters
These filters block traffic based on the frame's source MAC address, destination
MAC address, or both source and destination MAC addresses in flow bridging
mode. Address filters are always configured and applied to the input port.
• Port-to-address lock filters
These filters prohibit a user connected to a lock ed port or set of ports from using an-
other port .
• Static entry filters
These filters allow or force traffic to go to a set of destination ports based on a
frame's source MAC address, destination MAC address, or both source and destination MAC addresses in flow bridging mode. Static entries are always configured an d
applied at the input port.
• Secure port filters
A secure filter shuts down access to the SSR based on MAC addresses. All packets
received by a port are dropped. When combined with static entries, however, these
filters can be used to drop all received traffic but allow some frames to go through.
2 - 10 SSR User Reference Manual
Page 47
Monitor Bridging
The SSR provides display of bridging statistics and configurations contained in the
SSR.
To display bridging information, enter the following commands in Enable mode.
Chapter 2: Bridging Configuration Guide
Show IP routing table.
Show all MAC addresses currently in
the l2 tables.
Show l2 table information on a specific
port.
Show information the master MAC
table.
Show information on a specific MAC
address.
Show information on MACs registered.
Show al l VLANs.
Configuration Ex amples
Creating an IP or IPX VLAN
ip show routes
l2-tables show all-macs
l2-tables show port-macs
l2-tables show mac-table-stats
l2-tables show mac
l2-table show bridge-management
vlan list
VLANs are used to associate physical ports on the SSR with connected hosts that may
be physically separated but need to participate in the sam e broadcast domain. To
associate ports to a VLAN, you must first create an IP or IPX VLAN and then assign
ports to the VLAN.
For example, servers connected to port gi.1.(1-2) on the SSR need to communicate
with clients connected to et.4.(1-8). You can associate all the ports containing the
clients and servers to an IP VLAN called ‘BLUE’.
Step 1: Create an IP VLAN named ‘BLUE’
ssr(config)# vlan create BLUE ip
Step 2: Assign ports to the ‘BLUE’ VLAN.
SSR User Reference Manual 2 - 11
Page 48
Chapter 2: Bridging Configuration Guide
ssr(config)# vlan add ports et.1.(1-8),gi.1.(1-2) to BLUE
2 - 12 SSR User Reference Manual
Page 49
Chapter 3
g
Chapter 3 IP Routing Configuration Guide
This chapter describes how to configure IP interfaces and general non-protocolspecific routing parameters.
IP Routing Overview
Internet Protocol (IP) is a packet-bas ed protocol used to exc hange data over computer
networks. I P handles addressing, routing, f ragmentation, r eassembly, and protocol
demultiplexing. In addition, IP specifies how hosts and routers should process packets,
handle errors an d discar d packets. IP f orms the foundat ion upon which tr ansport layer
protocols, suc h as TCP or UDP, interoperate over a routed network.
The Transmission Control Protocol (TCP) is built upon the IP layer. TCP is a
connection-oriented protocol that specifies the data format, buffering and
acknowledgments used in the trans fer of dat a. TC P is a full -d uplex connection which
also specifies the procedures that the computers use to ensure that the data arrives
correctly.
The User Datagram Protocol (UDP) provides the pr imary mechanism that applications
use to send datagrams to other application pro grams. UDP is a connectionles s protocol
that does not guarantee delivery of datagrams between applications. Applications
which use UDP are responsible for ensuring successful data transfer by employing
error handling, retransmission and sequencing techniques.
TCP and UDP also specify “ports,” which identify the application which is using TCP/
UDP. For example, a web server would typically use TCP/UDP port 80, which
specifies HTTP-type traffic.
The SSR supports standards based TCP, UDP, and IP.
IP Routing Protocols
The SSR supports standards based unicast and multicast routing. Unicast routing
protocol support i nclude Int erio r Gateway Pr otocols and Ext erior Gate way Protoco ls.
Multicast routing protocols are used to determine how multicast data is transferred in
a routed environment.
Unicast Routin
Protocols
Interior Gateway Protocols are used for routing networks that are within an
“autonomous system,” a network of relativel y limited size. All IP interior gateway
protocols must be specified with a list of associated networks before routing activities
can begin. A routing process listens to updates from other routers on these networks
Page 50
Chapter 3: IP Routing Configuration Guide
and broadcasts its o wn routing infor mation on those same networks. The SSR s upports
the following Interior Gateway Protocols:
• Routing Information Protocol (RIP) Version 1, 2 (RFC 1058, 1723)
• Open Shortest Path First (OSPF) Version 2 (RFC 1583)
Exterior Gateway Protocols are used to transfer information between different
“autonomous systems”. The SSR supports the following Exterior Gateway Protocol:
• Border Gateway Protocol (BGP) Version 3, 4 (RFC 1267, 1771)
Multicast Routing Protocols
IP multicasting allows a host to send traffic to a subset of all hosts. These hosts
subscribe to group membership, thus notifying the SSR of participation in a multicast
transmission.
Multicast routing protocols are used to determine which routers have directly attached
hosts, as specified by IGMP, that have membership to a multicast session. Once host
memberships are determined, routers use multicast ro uting protocols, such as DVMRP,
to forward multicast traffic between routers.
The SSR supports the following multicast routing protocols:
• Distance Vector Multicast Routing Protocol (DVMRP) RFC 1075
• Internet Group Management Protocol (IGMP) as described in RFC 2236
The SSR also supports the latest DVMRP Version 3.0 draft specification, which
includes mtrace, Generation ID and Pruning/Grafting.
Configuring IP Interfaces and Parameters
This section provides an overview of configuring various IP parameters and setting up
IP interfaces.
Configure IP Addresses to Ports
Y ou can configure one IP interface d irectly to physical ports. Each port can be assigned
multiple IP addresses representing multiple subnets connected to the physical port.
To configure an IP interface to a port, enter one of the following commands in
Configure mode.
Configure an IP interface to a physical
port.
interface create ip
address-mask
<InterfaceName>
<ipAddr-mask>
port
<port>
3 - 2 SSR User Reference Manual
Page 51
Chapter 3: IP Routing Configuration Guide
Configure a secondary address to an
existing IP interface.
interface add ip
address-netmask
[broadcast
Configure IP Interfaces for a VLAN
Y o u can configure one IP interface per VLAN. Once an IP interface has been assigned
to a VLAN, you can add a secondary IP addresses to the VLAN.
T o configure a VLAN with an IP interface, enter the following command in Configure
mode:
Create an IP interface for a VLAN.
Configure a secondary address to an
existing VLAN.
interface create ip
address-mask
interface add ip
address-netmask
<name>
vlan
Specify Ethernet Encapsulation Method
The SmartSwitch Router supports two encapsulation types for IP. You can configure
encapsulation type on a per interface basis.
<InterfaceName>
<ipAddr-mask>
<i
r>
padd
<ipAddr-mask>
<InterfaceName>
]
<InterfaceName>
<ipAddr-mask>
vlan
<name>
• Ethernet II: The standard ARPA Ethernet Version 2.0 encapsulation, which uses a
16-bit protocol type code (the default encapsulation method)
• 802.3 SNAP: SNAP IEEE 802.3 encapsulation, in which the type code becomes the
frame length for the IEEE 802.2 LLC en capsulation (destination and source Serv ice
Access Points, and a control byte)
To configure IP encapsulation, enter one of the following commands in Configure
mode.
Configure Ethernet II encapsul at ion.
Configure 802.3 SNAP encapsulation.
interface create ip
output-mac-encapsulation ethernet_II
interface create ip
put-mac-encapsulation ethernet_snap
Configure Address Resolution Protocol
The SSR allows you to configure Address Resolution Protocol (ARP) table entries and
parameters. ARP is used to associate IP addresses with media or MAC addresses.
Taking an IP address as input, ARP determines the associated MAC address. Once a
media or MAC address is determined, the IP address/media address association is
<InterfaceName>
<InterfaceName>
out-
SSR User Reference Manual 3 - 3
Page 52
Chapter 3: IP Routing Configuration Guide
stored in an ARP cache for rapid retrieval. Then the IP datagram is encapsulated in a
link-layer frame and sent over the network.
Configure ARP Cache Entries
You can add and delete entries in the ARP cache. To add or delete static ARP entries,
enter one of the the following commands in Configure mode:
Add a static ARP entry.
Clear a static ARP entry.
Configure Proxy ARP
The SSR can be configured for proxy ARP. The SSR uses proxy ARP (as defined in
RFC 1027) to help hos ts with no knowled ge of routin g determi ne the MAC addr ess of
hosts on other networks or subnets. Th rough Proxy ARP, the SSR will resp ond to ARP
requests from a host with a ARP reply packet containing the SSR MAC address. Proxy
ARP is enabled by default on the SSR.
To disable proxy ARP, enter the following command in Configure mode:
Disable Proxy ARP on an interface.
Configure DNS Parameters
The SSR can be configured to specify DNS servers which supply name services for
DNS requests. You can specify up to three DNS servers.
arp add
port
arp clear
ip disable-proxy-arp interface
<host>
<port>
Name>
mac-addr
<host>
|all
<MAC-addr>
exit-
<Interface-
To configure DNS servers, enter the following command in Configure mode:
Configure a DNS server.
Y ou can also specify a domain name for the SSR. The domain name is used by the SSR
to respond to DNS requests.
To configure a domain name, enter the following command in Configure mode:
Configure a domain name.
3 - 4 SSR User Reference Manual
system set dns server
<IPaddr>[,<IPaddr>[,<IPaddr>
system set dns domain
<name>
]]
Page 53
Configure IP Services (ICMP)
The SSR provides ICMP message capabilities including ping and traceroute. Ping
allows you to determine the reachability of a certain IP host. Traceroute allows you to
trace the IP gateways to an IP host.
To access ping or traceroute on the SSR, enter the following commands in Enable
mode:
Chapter 3: IP Routing Configuration Guide
Specify ping.
Specify traceroute.
Monitor IP Parameters
The SSR provides display of IP statistics and configurations contained in the routing
table. Information displayed provides routing and performance information.
To display IP information, enter the following command in Enable mode:
Show ARP table entries.
Show ARP table settings.
Show IP interface configuration
Show all TCP/UDP connections and
services.
ping
size
wait
traceroute
<num>
<num>
[noroute]
arp show entries
arp show settings
interface show ip
ip show connections [no-lookup]
<hostname-or-IPaddr>
<num>
<num>
] [size
] [wait-time
[flood] [dontroute]
<host>
[max-ttl
<num>
] [source
<secs>
] [verbose]
packets
<num>
<secs>
<num>
] [probes
] [tos
Show configuration of IP interfaces.
Show IP routing table information.
Show ARP entries in routing table.
Show DNS parameters.
SSR User Reference Manual 3 - 5
ip show interfaces [
ip show routes
ip show routes show-arps
system show dns
<interface-name>
]
Page 54
Chapter 3: IP Routing Configuration Guide
Configuration Ex amples
Assigning IP/IPX Interfaces
To enable routing on the SSR, you must assign an IP or IPX interface to a VLAN. To
assign an IP or IPX interface named ‘RED’ to the ‘BLUE’ VLAN, perform the
following:
ssr(config)# interface create ip RED address-netmask 10.50.0.1/
255.255.0.0 vlan BLUE
You can also assign an I P or I PX interface dir ectly to a physical po rt. For example, to
assign an IP interface ‘RED’ to physical port et.3.4, perform the following:
ssr(config)# interface create ip RED address-netmask 10.50.0.0/
255.255.0.0 port et.3.4
3 - 6 SSR User Reference Manual
Page 55
Chapter 4 RIP Configuration Guide
RIP Overview
This chapter describes how to configure Routing Information Protocol (RIP) in the
SmartSwitch Router. RIP is a distance-vector routing protocol for use in small
networks. RIP is described in RFC 1723. A router running RIP broadcasts updates at
set intervals. Each update contains paired values where each pair consists of an IP
network address and an integer distance to that network. RIP uses a hop count metric
to measure the distance to a destination.
The SmartSwitch Router provides support for RIP Version 1 and 2. The SSR
implements plain text and MD5 authentication methods for RIP Version 2.
The protocol independent features that apply to RIP are described in the section “IP
Routing Configuration Guide” on page 3 - 1.
Chapter 4
Configure RIP
By default, RIP is disabled on the SSR and on each of the attached interfaces. To
configure RIP on the SSR, follow these steps:
1. Start the RIP process by using the rip start command.
2. Use the rip add interface command to inform RIP about the attached interfaces.
Enabling and Disabling RIP
To enable or disable RIP, enter one of the following commands in Configure mode.
Enable RIP.
Disable RIP.
Configuring RIP Interfaces
To configure RIP in the SSR, you must first add interfaces to inform RIP about
attached interfaces.
rip start
rip stop
Page 56
Chapter 4: RIP Configuration Guide
To add RIP interfaces, enter the following commands in Configure mode.
Add interfaces to the RIP process.
Add gateways from which the SSR will
accept RIP updates.
Define the list of routers to which RIP
sends packets di rect ly, not through multicast or broadcast.
Configure RIP Parameters
No further configuration is required and the system default parameters will be used by
RIP to exchange routing information. These default parameters may be modified to
suit your needs by using the rip set interface command.
RIP Parameter Default Value
Version number RIP v1
Check-zero for RIP reserved parame-
ters
rip add interface
rip add trusted-gateway
IPaddr>
rip add source-gateway
IPaddr>
<interfacename-or-IPaddr>
Enabled
<interfacename-or-
<interfacename-or-
Whether RIP packets should be
Choose
broadcast
Preference for RIP routes 100
Metric for incoming routes 1
Metric for outgoing routes 0
Authentication None
Update interval 30 seconds
4 - 2 SSR User Reference Manual
Page 57
Chapter 4: RIP Configuration Guide
To change RIP parameters, enter the following commands in Configure mode.
Set RIP Versi on on an interface to
RIP V1 .
Set RIP Versi on on an interface to
RIP V2.
Specify that RIP V2 packets should be
multicast on this interface.
Specify that RIP V2 packets that are
RIP V1-compatible shoul d be broadcast
on this interface.
Change the metric on incoming RIP
routes.
Change the metric on outgoing RIP
routes.
Set the authentication method to simple
text up to 8 characters.
rip set interface
IPaddr>
rip set interface
IPaddr>
rip set interface
IPaddr>
rip set interface
IPaddr>
rip set interface
IPaddr>
rip set interface
IPaddr>
rip set interface
IPaddr>
|all version 1
|all version 2
|all type multicast
|all type broadcast
|all metric-in
|all metric-out
|all authentication-method simple
<interfacename-or-
<interfacename-or-
<interfacename-or-
<interfacename-or-
<interfacename-or-
<num>
<interfacename-or-
<num>
<interfacename-or-
Set the authentication method to MD5.
Specify the metric to be used when
rip set interface
IPaddr>
rip set default-metric
|all authentication-method md5
<interfacename-or-
<num>
advertising routes that were learned
from other protocols.
Configure RIP Route Preference
You can set the preference of routes learned from RIP.
To configure RIP route preference, enter the following command in Configure mode.
Set the preference of routes learned
rip set preference
<num>
from RIP.
Configure RIP Route Default-Metric
Y ou can def ine the metric used when advertising routes via RIP that were learned from
other protocols. The default value for this parameter is 16 (unreachable). To export
SSR User Reference Manual 4 - 3
Page 58
Chapter 4: RIP Configuration Guide
routes from other protocols into RIP, you must explicitly specify a value for the
default-metric parameter. The metric specified by the default-metric parameter may be
overridden by a metric specified in the export command.
To configure default-metric, enter the following command in Configure mode.
Define the metric used when advertising routes via RIP that were learned
from other protocols.
<num>
For
, you must specify a number between 1 and 16.
Monitoring RIP
The rip trace command can be used to trace all rip request and response packets.
To monitor RIP information, enter the following commands in Enable mode.
Show all RIP information.
Show RIP export polic i es.
Show RIP glob al information.
Show RIP import policies .
Show RIP information on the specified
interface.
rip set default-metric
rip show all
rip show export-policy
rip show globals
rip show import-policy
rip show interface
<Name or IP-addr>
<num>
Show RIP interface policy information.
Show detailed information of all RI P
packets
Show detailed information of all pack -
ets received by the router.
Show detailed information of all pack -
ets sent by the router.
Show detailed information of all
request received by the router.
4 - 4 SSR User Reference Manual
rip show interface-policy
rip trace packets detail
rip trace packets receive
rip trace packets send
rip trace request receive
Page 59
Chapter 4: RIP Configuration Guide
Show detailed information of all
response received by the router.
Show detailed information of respo ns e
packets sent by the router.
Show detailed information of request
packets sent by the router.
Show RIP timer information.
Configuration Ex ample
SSR 1 SSR 2
Interface 1.1.1.1 Interface 3.2.1.1
! Example configuration
!
! Create interface ssr1-if1 with ip address 1.1.1.1/16 on port
et.1.1 on SSR-1
interface create ip ssr1-if1 address-netmask 1.1.1.1/16 port
et.1.1
!
! Configure rip on SSR-1
rip add interface ssr1-if1
rip set interface ssr1-if1 version 2
rip start
!
!
! Set authentication method to md5
rip set interface ssr1-if1 authentication-method md5
!
! Change default metric-in
rip set interface ssr1-if1 metric-in 2
!
! Change default metric-out
rip set interface ssr1-if1 metric-out 3
rip trace response receive
rip trace response send
rip trace send request
rip show timers
SSR User Reference Manual 4 - 5
Page 60
Chapter 4: RIP Configuration Guide
4 - 6 SSR User Reference Manual
Page 61
Chapter 5
Chapter 5 OSPF Configuration Guide
OSPF Overview
Open Shortest Path First (OSPF) is a link-state routing protocol that supports IP
subnetting and aut hentication. The SSR supports OSPF Version 2.0 as defined in RFC
1583. Each link-state message contains all the links connected to the router with a
specified cost associated with the link.
The SSR supports the following OSPF functions:
• Stub Areas: D efinition of st ub areas is supported
• Authentication: Simple password and MD5 authentication methods are supported
within an area
• Virtual Links: Virtual links are supported
• Route Redistribution: Routes learned via RIP, BGP, or any other sources can be
redistributed into OSPF. OSPF routes can be redistributed into RIP or BGP
• Interface Parameters: Parameters that can be configured include interface output
cost, retransmission interval, interface transmit delay, router priority, router dead
and hello intervals, and authentication key
Configure OSPF
To configure OSPF on the SSR, you must enable OSPF, create OSPF areas, assign
interfaces to OSPF areas, and, if necessary, specify any of the OSPF interface
parameters.
To configure OSPF, you may need to perform some or all of the following tasks:
1. Enable OSPF.
2. Create OSPF areas.
3. Create an IP interface or assign an IP interface to a VLAN.
4. Add IP interfaces to OSPF areas.
5. Configure OSPF interface parameters, if necessary.
Note:
By default, the priority of an OSPF router for an interface is set to zero,
which makes the router ineligible from becoming a designated router on the
network to which the interface belongs. To make the router eligible to
become a designated router, you must set the priority to a non-zero value.
Page 62
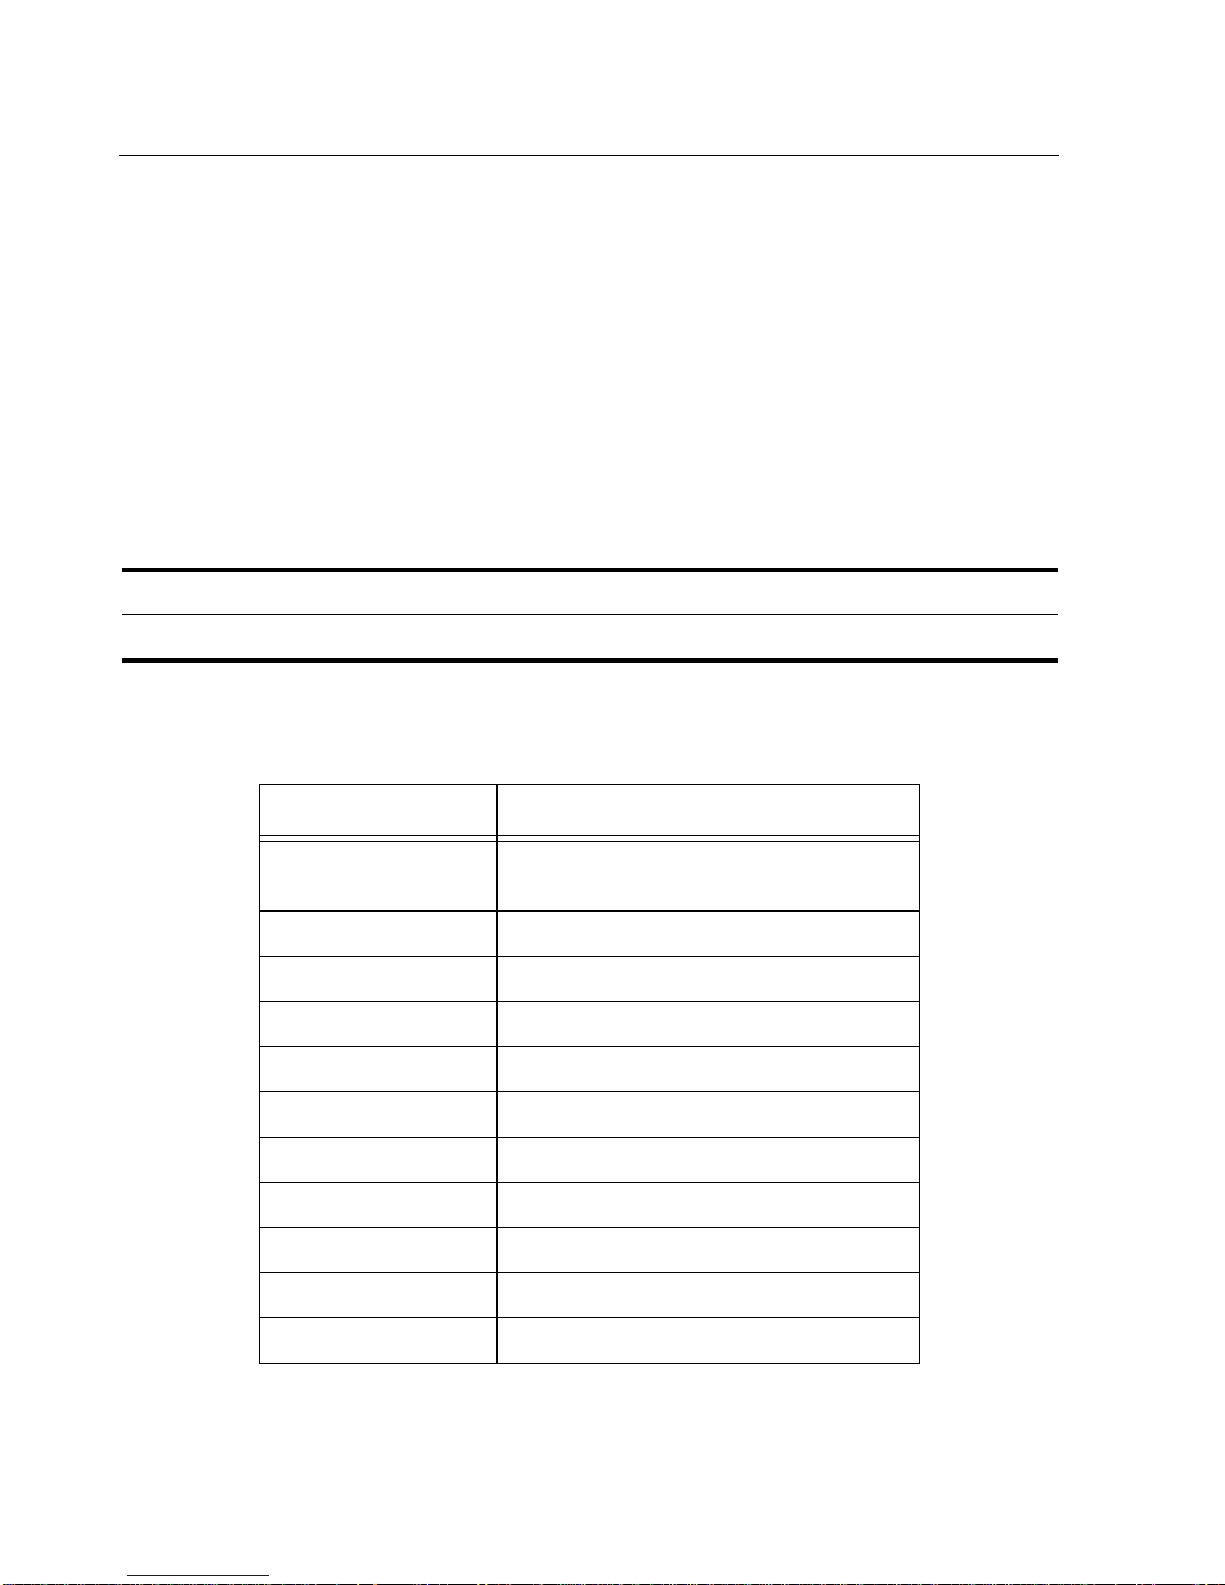
Chapter 5: OSPF Configuration Guide
The default cost of an OSPF interf ace is 1. The cost o f the interface should
be inversely proportional to the bandwidth of the interface; if the SSR has
interfaces with differing bandwidths, the OSPF costs should be set
accordingly.
6. Add IP networks to OSPF areas.
7. Create virtual links, if necessary.
Enable OSPF
OSPF is disabled by default on the SSR.
To enable or disable OSPF, enter one of the following commands in Configure mode.
Enable OSPF.
Disable OSPF.
ospf start
ospf stop
Configure OSPF Interface Parameters
You can configure the OSPF interface parameters shown in the table below.
OSPF Parameter Default Value
Interface OSPF State
(Enable/Disable)
Cost 1
No multicast Default is using multicast mechanism.
Retransmit interval 5 seconds
Transit delay 1 second
Priority 0
Hello interval 10 seconds (broadcast), 30 (non broadcast)
Enable (except for virtual links)
Router dead interval 4 times the hello interval
Poll Interval 120 seconds
Key chain N/A
Authentication Method None
5 - 2 SSR User Reference Manual
Page 63
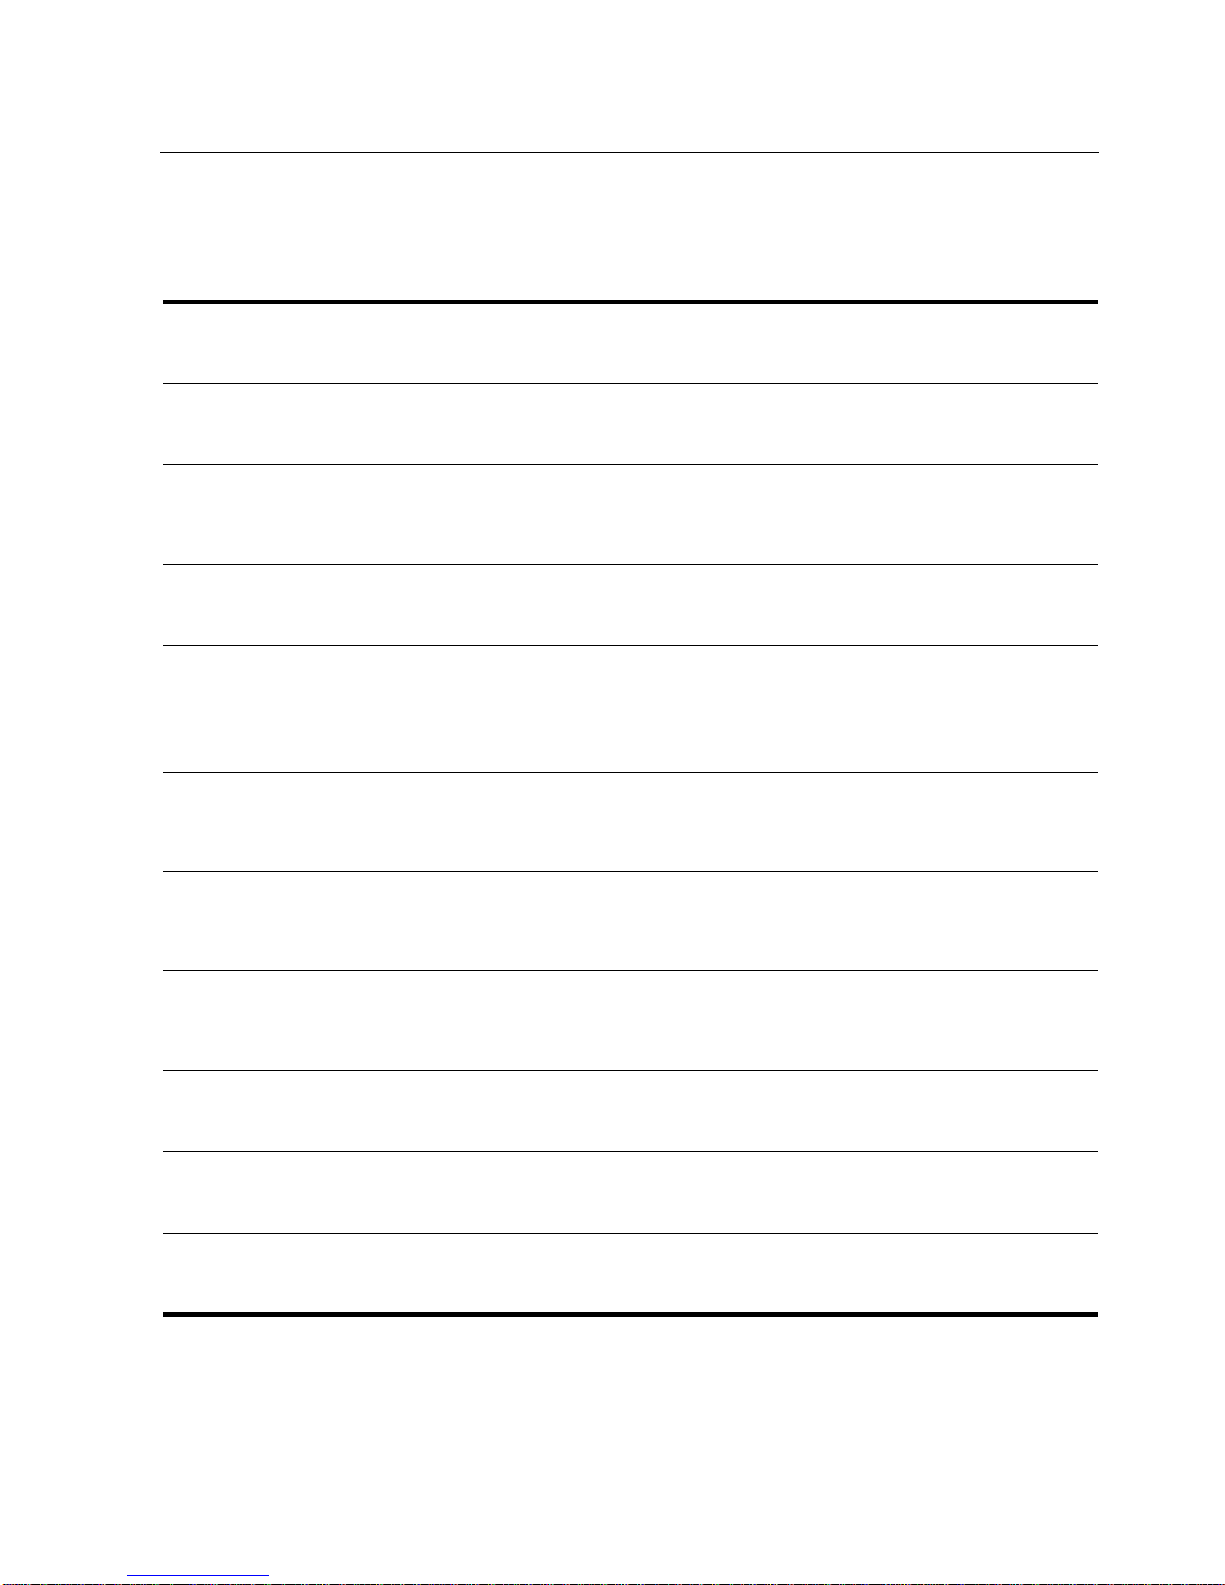
Chapter 5: OSPF Configuration Guide
To configure OSPF interface parameters, enter one of the following commands in
Configure mode:
Enable OSPF state on interface.
Specify the cost of sending a packet
on an OSPF interface.
Specify the priority for determining
the designated router on an OSPF
interface.
Specify the interval between OSPF
hello packets on an OSPF interface.
Configure the retransmission interval between link state advertisements
for adjacencies belonging to an
OSPF interface.
Specify the number of seconds
required to transmit a link state
update on an OSPF interface.
Specify the time a neighbor router
will listen for OSPF hello packets
before declaring the router down.
ospf set interface <
state disable|enable
ospf set interface <
<num>
ospf set interface <
priority
ospf set interface <
hello-interval
ospf set interface <
retransmit-interval
ospf set interface <
transit-delay
ospf set interface <
router-dead-interval
<num>
<num>
name-or-IPaddr
<num>
name-or-IPaddr
name-or-IPaddr
name-or-IPaddr
name-or-IPaddr
<num>
name-or-IPaddr
name-or-IPaddr
<num>
>|all
>|all cost
>|all
>|all
>|all
>|all
>|all
Disable IP multicast for sending
OSPF packets to neighbors on an
OSPF interface.
Specify the poll interval on an OSPF
interface.
Specify the identifier of the key chain
containing the authentication keys.
Specify the authentication method to
be used on this interface.
SSR User Reference Manual 5 - 3
ospf set interface <
multicast
ospf set interface <
poll-interval
ospf set interface <
chain
ospf set interface <
authentication-method none|simple|md5
<num-or-string>
<num>
name-or-IPaddr
name-or-IPaddr
name-or-IPaddr
name-or-IPaddr
>|all no-
>|all
>|all key-
>|all
Page 64
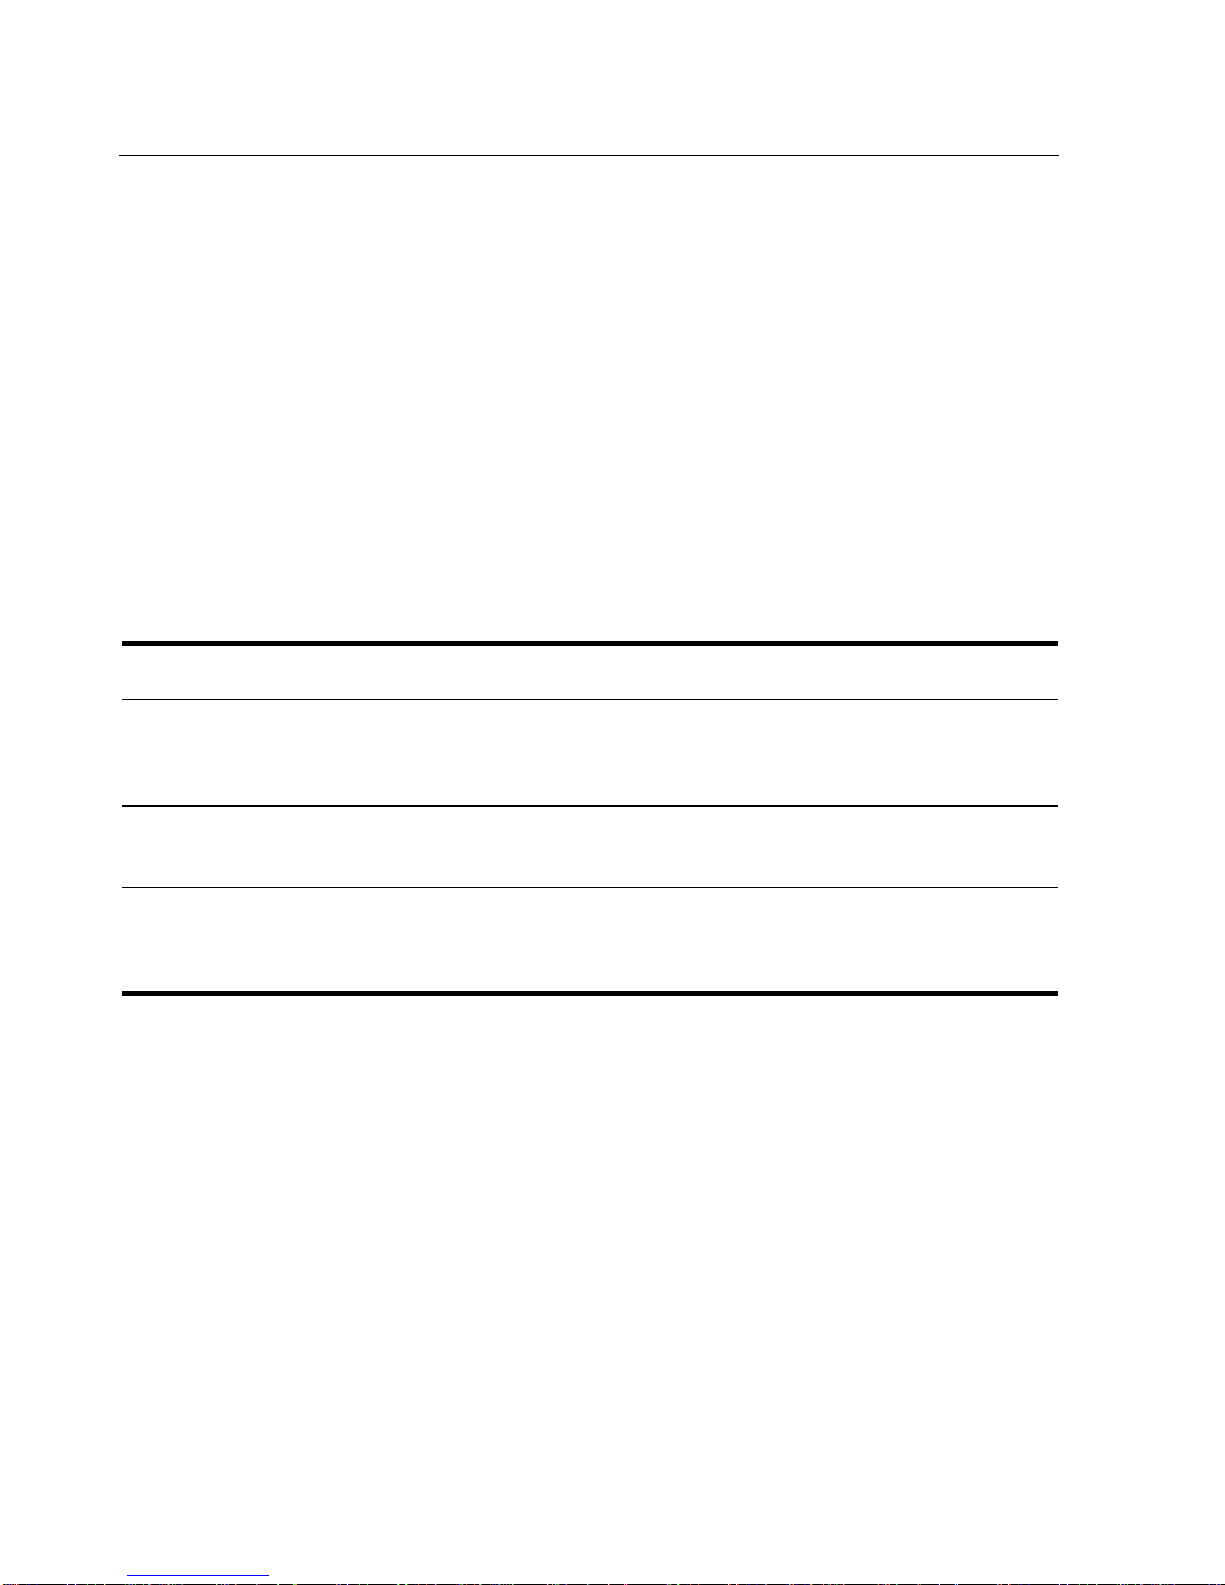
Chapter 5: OSPF Configuration Guide
Configure an OSPF Area
OSPF areas are a collection of subnets that are grouped in a logical fashion. These
areas communicate with other areas via the backbone area. Once OSPF areas are
created, you can add interfaces, stub hosts, and summary ranges to the area.
In order to reduce the amount of routing information propagated between areas, you
can configure summary-ranges on Area Border Routers (ABRs). On the SSR,
summary-ranges are created using the
specified using this command describe the scope of an area. Intra-area Link State
Advertisements (LSAs) that fall within the specified ranges are not advertised into
other areas as inter-area routes. Instead, the specified ranges are advertised as summary
network LSAs.
To create areas and assign interfaces, enter the following commands in the Configure
mode.
ospf add network
command – the networ ks
Create an OSPF area.
Add an interface to an OSPF area.
Add a stub host to an OSPF area.
Add a network to an OSPF area for
summarization.
ospf create area
ospf add interface <
[to-area
broadcast|non-broadcast]
ospf add stub-host [to-area
addr>
ospf add network
<area-addr>
net]
Configure OSPF Area Parameters
The SSR allows configuration of various OSPF area parameters, including stub areas,
stub cost and authentication method. Stub areas are areas into which information on
external routes is not sent. Instead, there is a default external route generated by the
ABR, into the stub area for destinations outside the autonomous system. Stub cost
specifies the cost to be used to inject a defau lt route into a stub area. An authen tication
method for OSPF packets can be specified on a per-area bas is.
<area-num>
name-or-IPaddr
<area-addr>
|backbone] [cost
|backbone] [restrict] [host-
|backbone] [type
<IPaddr/mask>
<num>
|backbone
>
<area-
]
[to-area
5 - 4 SSR User Reference Manual
Page 65
Chapter 5: OSPF Configuration Guide
To configure OSPF area parameters, enter the following commands in the Configure
mode.
Specify an OSPF stub area.
Specify the cost to be used to inject a
default route into an area.
Specify the authentication method to be
used by neighboring OSPF routers.
Create Virtual Links
In OSPF, virtual links can be established:
• To connect an area via a transit area to the backbone
• To create a redundant backbone connection via another area
Each Area Border Router must be configured with the same virtual link. Note that
virtual links cannot be configured through a stub area.
To configure virtual links, enter the following commands in the Configure mode.
Create a virtual link.
ospf set area
ospf set area
ospf set area
[authentication-method none|simple|md5]
ospf add virtual-link
[neighbor
num>
]
<area-num>
<area-num>
<area-num>
<IPaddr>]
stub
stub-cost
[stub]
<number-or-string>
[transit-area
<area-
<num>
Set virtual link pa rameters.
ospf set virtual-link
[state disable|enable] [cost
[retransmit-interval
<num>
<num>
interval
] [priority
] [router-dead-interval
<num>
<num>
]
<number-or-string>
<num>
]
<num>
] [transit-delay
] [hello-interval
<num>
] [poll-
SSR User Reference Manual 5 - 5
Page 66
Chapter 5: OSPF Configuration Guide
Configure Autonomous System External (ASE) Link
Advertisements
These parameters specify the defaults used when importing OSPF AS External (ASE)
routes into the routing table and exporting routes from the routing table into OSPF
ASEs.
T o specify AS external link advertisements parameters, enter the following commands
in the Configure mode:
Specify the interval which AS external
ospf set export-interval
<num>
link advertisements will be gene rated
and flooded to an OSPF AS.
Specify the number of AS external link
ospf set export-limit
<num>
advertisements which will be generated
and flooded to an OSPF AS.
Specify AS external link advertisement
default parameters.
ospf set ase-defaults [preference
[cost
[type
<num>
<num>
]
] [inherit-metric]
Configure OSPF over Non-Broadcast Multiple Access
You can configure OSPF over NBMA circuits to limit the number of Link State
Advertisements (LSAs). LSAs are limited to initial advertisements and any subsequent
changes. Periodic LSAs over NBMA circuits are suppressed.
To configure OSPF over WAN circuits, enter the following command in Configure
mode:
Configure OSPF over a WAN circuit.
ospf add nbma-neighbor
IPaddr>
[eligible]
to-interface <
<hostname-or-
name-or-IPaddr>
<num>
]
Monitoring OSPF
The SSR provides display of OSPF statistics and configurations contained in the
routing table. Information displayed provides routing and performance information.
5 - 6 SSR User Reference Manual
Page 67
Chapter 5: OSPF Configuration Guide
To display OSPF information, enter the following commands in Enable mode.
Show IP routing table.
Monitor OSPF error conditions.
Show information on all interfaces configured for OSPF.
Display link state advertisement information.
Display the link state database.
Shows information about all OSPF
routing neighbors.
Show information on valid next hops.
Display OSPF routing table.
ip show table routing
ospf monitor errors destination
or-IPaddr>
ospf monitor interfaces destination
<hostname-or-IPaddr>
ospf monitor lsa destination
IPaddr>
ospf monitor lsdb destination
or-IPaddr>
ospf monitor neighborsdestination
<hostname-or-IPaddr>
ospf monitor next-hop-list destination
<hostname-or-IPaddr>
ospf monitor routes destination
or-IPaddr>
<hostname-
<hostname-or-
<hostname-
<hostname-
Monitor OSPF statistics for a specified
destination.
Shows information about all OSPF
ospf monitor statistics destination
<hostname-or-IPaddr>
ospf monitor version
routing version
Shows OSPF Autonomous System
ospf sbow AS-External-LSDB
External Link State Database.
Show all OSPF tables.
Show all OSPF areas.
Show OSPF errors.
Show information abou t OSP F export
ospf show all
ospf show areas
ospf show errors
ospf show export-policies
policies.
SSR User Reference Manual 5 - 7
Page 68
Chapter 5: OSPF Configuration Guide
Shows routes redistributed into OSPF.
Show all OSPF global parameters.
Show information abou t OSP F impo rt
policies.
Show OSPF interfaces.
Shows information about all valid next
hops mostly derived from the SPF calculation.
Show OSPF statistics.
Shows information about OSPF Border
Routes.
Show OSPF timers.
Show OSPF virtual-links.
ospf show exported-routes
ospf show globals
ospf show import-policies
ospf show interfaces
ospf show next-hop-list
ospf show statistics
ospf show summary-asb
ospf show timers
ospf show virtual-links
OSPF Configurat ion Examples
For all examples in this section, refer to the configuration shown in Figure 1 on page
5 - 12.
The following configuration commands for router R1:
• Determine the IP address for each interface
• Specify the static routes configured on the router
• Determine its OSPF configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 140.1.3.1/24 port et.1.6
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.1.1.2
5 - 8 SSR User Reference Manual
Page 69
ip add route 160.1.5.0/24 gateway 120.1.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf start
ospf create area 140.1.0.0
ospf create area backbone
ospf set ase-defaults cost 4
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Interface Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf add interface 140.1.1.1 to-area 140.1.0.0
ospf add interface 140.1.2.1 to-area 140.1.0.0
ospf add interface 140.1.3.1 to-area 140.1.0.0
ospf add interface 130.1.1.1 to-area backbone
Exporting all interface and static routes to OSPF
Router R1 has several static routes. We would export these static routes as type-2
OSPF routes. The interface routes would be redistributed as type-1 OSPF routes.
Chapter 5: OSPF Configuration Guide
1. Create a OSPF export destination for type-1 routes since we would like to redis-
tribute certain routes into OSPF as type 1 OSPF-ASE routes.
ip-router policy create ospf-export-destination
ospfExpDstType1 type 1 metric 1
2. Create a OSPF export destination for type-2 routes since we would like to redis-
tribute certain routes into OSPF as type 2 OSPF-ASE routes.
ip-router policy create ospf-export-destination
ospfExpDstType2 type 2 metric 4
3. Create a Static export source since we would like to export static routes.
ip-router policy create static-export-source statExpSrc
4. Create a Direct export source since we would like to export interface/direct r outes.
ip-router policy create direct-export-source directExpSrc
5. Create the Export-Policy for redistributing all interface routes and static routes
into OSPF.
ip-router policy export destination ospfExpDstType1 source
directExpSrc network all
ip-router policy export destination ospfExpDstType2 source
statExpSrc network all
Export all RIP, interface, and static routes to OSPF.
Note:
Also export interface, static, RIP, OSPF, and OSPF-ASE routes into RIP.
SSR User Reference Manual 5 - 9
Page 70
Chapter 5: OSPF Configuration Guide
In the configur ation sho wn in Fig ure 1 on p age 5 - 12, suppos e if we decide to run R IP
Version 2 on network 120.190.0.0/16, connecting routers R1 and R2.
W e would like to redistribute these RIP routes as OSPF type-2 routes, and associate the
tag 100 with them. Router R1 would also like to redistribute its static routes as type 2
OSPF routes. The interface routes would redistributed as type 1 OSPF routes.
Router R1 would like to redistribute its OSPF, OSPF-ASE, RIP, Static and Interface/
Direct routes into RIP.
1. Enable RIP on interface 120.190.1.1/16.
rip add interface 120.190.1.1
rip set interface 120.190.1.1 version 2 type multicast
2. Create a OSPF export destination for type-1 routes.
ip-router policy create ospf-export-destination
ospfExpDstType1 type 1 metric 1
3. Create a OSPF export destination for type-2 routes.
ip-router policy create ospf-export-destination
ospfExpDstType2 type 2 metric 4
4. Create a OSPF export destination for type-2 routes with a tag of 100.
ip-router policy create ospf-export-destination
ospfExpDstType2t100 type 2 tag 100 metric 4
5. Create a RIP export source.
ip-router policy export destination ripExpDst source
ripExpSrc network all
6. Create a Static export source.
ip-router policy create static-export-source statExpSrc
7. Create a Direct export source.
ip-router policy create direct-export-source directExpSrc
8. Create the Export-Policy for redistributing all interface, RIP and static routes into
OSPF.
ip-router policy export destination ospfExpDstType1 source
directExpSrc network all
ip-router policy export destination ospfExpDstType2 source
statExpSrc network all
ip-router policy export destination ospfExpDstType2t100
source ripExpSrc network all
9. Create a RIP export destination.
5 - 10 SSR User Reference Manual
Page 71
Chapter 5: OSPF Configuration Guide
ip-router policy create rip-export-destination ripExpDst
10. Create OSPF export source.
ip-router policy create ospf-export-source ospfExpSrc type OSPF
11. Create OSPF-ASE export source.
ip-router policy create ospf-export-source ospfAseExpSrc type
OSPF-ASE
12. Create the Export-Policy for redistributing all interface, RIP, static, OSPF and
OSPF-ASE routes into RIP.
ip-router policy export destination ripExpDst source
statExpSrc network all
ip-router policy export destination ripExpDst source
ripExpSrc network all
ip-router policy export destination ripExpDst source
directExpSrc network all
ip-router policy export destination ripExpDst source
ospfExpSrc network all
ip-router policy export destination ripExpDst source
ospfAseExpSrc network all
SSR User Reference Manual 5 - 11
Page 72
5 - 12 SSR User Reference Manual
Figure 1: Exporting to OSPF
BGP
R1
R2
R3
R41
A r e a B a c k b o n e
A r e a 140.1.0.0
(RIP V2)
140.1.1.1 /24
140.1.2.1/24
140.1.5/24
190.1.1.1/16
120.190.1.1/16
160.1.5.2/24
R10
R5 R7
202.1.2.2/16
140.1.3.1/24
130.1.1.1/16
R8
A r e a 150.20.0.0
150.20.3.1/16
150.20.3.2/16
140.1.1.2/24
130.1.1.3/16
120.190.1.2/16
160.1.5.2/24
Page 73
Chapter 6
Chapter 6 Routing Policy Configuration Guide
Route Import and Export Policy Overview
The SSR family of routers supports extremely flexible routing policies. The SSR
allows the network administrator to control import and export of routing information
based on criteria including:
• Individual protocol
• Source and destination autonomous system
• Source and destination interface
• Previous hop router
• Autonomous system path
• Tag associated with routes
• Specific destination address
The network administrator can specify a preference level for each combination of
routing information being imported by using a flexible masking capability.
Preference
The SSR also provides the ability to create advanced and simple routing policies.
Simple routing policies provide a quick route redistribution between various routing
protocols (RIP and OSPF). Ad vanced routi ng policies provide mo re control ov er route
redistribution.
Preference is the value the SSR routing process uses to order preference of routes from
one protocol or peer over another. Preference can be set using several different
configuration commands. Preference can be set based on one network interface over
another, from one protocol over another, or from one remote gateway over another.
Preference may not be used to control the selection of routes within an Interior
Gateway Protocol (IGP) This is accomplished automatically by the protocol based on
metric.
Preference may be used to select routes from the same Exterior Gateway Protocol
(EGP) learned from different peers or autonomous systems. Each route has only one
preference value associated with it, even though the preference can be set at many
places using configuration commands. The last or most specific preference value set
for a route is the value used. A preference value is an arbitrarily assigned value used
to determine the order of routes to the same destination in a single routing database.
The active route is chosen by the lowest preference value.
Page 74
Chapter 6: Routing Policy Configuration Guide
A default preference is assigned to each source from which the SSR routing process
receives routes. Preference values range from 0 to 255 with the lowest number
indicating the most preferred route.
The following table summarizes the default preference values for routes learned in
various ways. The table lists the CLI commands that set preference, and shows the
types of routes to which each CLI command applies. A default pref erence for each type
of route is listed, and the table notes preference precedence between protocols. The
narrower the scope of the statement, the higher precedence its preference value is
given, but the smaller the set of routes it affects.
Preference of Defined by CLI Command Default
Direct connected networks ip-router global set interface 0
OSPF routes ospf 10
Static routes from config ip add route 60
RIP routes rip set preference 100
Point-to-point interface 110
Routes to interfaces that are
down
Aggregate/generate routes aggr-gen 130
OSPF AS external routes ospf set ase-defaults preference 150
BGP routes bgp set preference 170
Import Policies
Import policies control the importation of routes from routing protocols and their
installation in the routing databases (Routing Information Base and Forwarding
Information Base). Import Policies determine which routes received from other
systems are used by the SSR routing process. Every import policy can have up to two
components:
• Import-So urce
• Route-Filter
ip-router global set interface
down-preference
120
6 - 2 SSR User Reference Manual
Page 75
Import-Source
Chapter 6: Routing Policy Configuration Guide
This component specifies the source of the imported routes. It can also specify the
preference to be associated with the routes imported from this source.
The routes to be imported can be identified by their associated attributes:
• Type of the source protocol (RIP, OSPF, BGP).
• Source interface or gateway from which the route was received.
• Source autonomous system from which the route was learned.
• AS path associated with a route. Besides autonomous system, BGP also supports
importation of routes using AS path regular expressions, and AS path options.
If multiple communities are specified using the optional-attributes-list, only updates
carrying all of the specified communities will be matched. If the specified optionalattributes-list has the value none for the well-known-community option, then only
updates lacking the community attribute will be matched.
In some cases, a combination of the associated attributes can be specified to identify
the routes to be imported.
Note:
It is quite possible for several BGP import policies to match a given update.
If more than one policy matches, the first matching policy will be used. All
later matching policies will be ignored. For this reason, it is generally desirable to order import policies from most to least specific. An import policy
with an optional-attributes-list will match any update with any (or no) communities.
The importation of RIP routes may be controlled by source interface and source
gateway. RIP does not support the use of preference to choose between RIP routes.
That is left to the protocol metrics.
Due to the nature of OSPF, only the importation of ASE routes may be controlled.
OSPF intra-and inter-area routes are always imported into the routing table with a
preference of 10. If a tag is specified with the import policy, routes with the specified
tag will only be imported.
It is only possible to restrict the importation of OSPF ASE routes when functioning as
an AS border router.
Like the other interior protocols, preference cannot be used to choose between OSPF
ASE routes. That is done by the OSPF costs.
SSR User Reference Manual 6 - 3
Page 76
Chapter 6: Routing Policy Configuration Guide
Route-Filter
This component specifies the individual routes which are to be imported or restricted.
The preference to be associated with these routes can also be explicitly specified using
this component.
The preference associated with the imported routes are inherited unless explicitly
specified. If there is no preference specified with a route-filter, then the preference is
inherited from the one specified with the import-source.
Every protocol (RIP, OSPF, and BGP) has a configurable parameter that specifies
default-preference associated with routes imported to that protocol. If a preference is
not explicitly specified with the route-filter, as well as the import-source, then it is
inherited from the default-preference associated with the protocol for which th e routes
are being imported.
Export Policies
Export policies control the redistribution of routes to other systems. They determine
which routes are advertised by the Unicast Routing Process to other systems. Every
export policy can have up to three components:
• Export-Destination
• Export-Source
• Route-Filter
Export-Destination
This component specifies the destination where the routes are to be exported. It also
specifies the attributes associated with the exported routes. The interface, gateway or
the autonomous system to which the routes are to be redistributed are a few examples
of export-destinations. The metric, type, tag, and AS-Path are a few examples of
attributes associated with the exported routes.
Export-Source
This component specifies the source of the exported routes. It can also specify the
metric to be associated with the routes exported from this source.
The routes to be exported can be identified by their associated attributes:
• Their protocol type (RIP, OSPF, BGP, Static, Direct, Aggregate).
• Interface or the gateway from which the route was received.
• Autonomous system from which the route was learned.
• AS path associated with a route. When BGP is configured, all routes are assigned an
AS path when they are added to the routing table. For interior routes, this AS path
6 - 4 SSR User Reference Manual
Page 77
Route-Filter
Chapter 6: Routing Policy Configuration Guide
specifies IGP as the origin and no ASs in the AS path ( the current AS is added when
the route is exported). For BGP routes, the AS path is stored as learned from BGP.
• Tag associated with a route. Both OSPF and RIP version 2 currently support tags.
All other protocols have a tag of zero.
In some cases, a combination of the associated attributes can be specified to identify
the routes to be exported.
This component specifies the individual routes which are to exported o r restricted. The
metric to be associated with these routes can also be explicitly specified using this
component.
The metric associated with the exported routes are inherited unless explicitly specified.
If there is no metric specified with a route-filter, then the metric is inherited from the
one specified with the export-source.
If a metric was not explicitly specified with both the route-filter and the export-sour ce,
then it is inherited from the one specified with the export-des tination.
Every protocol (RIP, OSPF, and BGP) has a configurable parameter that specifies
default-metric associated with routes exported to that protocol. If a metric is not
explicitly specified with the route-filter, export-source as well as export-destination,
then it is inherited from the default-metric associated with the pr otocol to which the
routes are being exported.
Specifying a Route Filter
Routes are filtered by specifying a route-filter that will match a certain set of routes by
destination, or by destination and mask. Among other places, route filters are used with
martians and in import and export policies.
The action taken when no match is found is dependent on the context. For instance, a
route that does match any of the route-filters associated with the specified impo rt or
export policies is rejected.
A route will match the most specific filter that applies. Specifying more than one filter
with the same destination, mask and modifiers generates an error.
There are three possible formats for a route filter. Not all of these formats are available
in all places. In most cases, it is possible to associate additional op tions with a filter.
For example, while creating a martian, it is possible to specify the allow option, while
creating an import policy, one can specify a pref er ence, and while cre ating an exp ort
policy one can specify a metric.
SSR User Reference Manual 6 - 5
Page 78
Chapter 6: Routing Policy Configuration Guide
The three forms of a route-filter are:
• Network [ exact | refines | between number,number]
• Network/mask [ exact | refines | between number,number]
• Network/masklen [ exact | refines | between number,number]
Matching usually requires both an address and a mask, although the mask is implied
in the shorthand forms listed below. These three forms vary in how the mask is
specified. In the first form, the mask is implied to be the natural mask of the network.
In the second, the mask is explicitly specified. In the third, the mask is specified by the
number of contiguous one bits.
If no optional parameters (exact, refines, o r between) are specified, any destination that
falls in the range given by the network and mask is matched, so the mask of the
destination is ignored. If a natural network is specified, the network, any subnets, and
any hosts will be matched. Three optional param e ters that cause the mask of the
destination to also be considered are:
• Exact: Specifies that the mask of the destination must match the supplied m a sk
exactly. This is used to match a network, but no subnets or hosts of that network.
• Refines: Specifies that the mask of the destination must be more specified (i.e.,
longer) than the filter mask. This is used to match subnets an d/or hosts of a network,
but not the network.
• Between number, number: Specifies that the mask of the destination must be as or
more specific (i.e., as long as or longer) than the lower limit (the first number
parameter) and no more specific (i.e., as long as or shorter) than the upper limit (the
second number). Note that exact and refines are both special cases of between.
Aggregates and Generates
Route aggregation is a method of generating a more general route, given the presence
of a specific route. It is used, for example, at an autonomous system border to generate
a route to a network to be advertised via BGP given the presence of one or more
subnets of that network learned via OSPF. The routing process does not perform any
aggregation unless explicitly requested .
Route aggregation is al so used by regional and nat ional networks to re duce the amount
of routing info rmation passe d aroun d. With careful allocati on of networ k addres ses to
clients, regional netwo rks can just announce one rout e to regional networ ks instead of
hundreds.
Aggregate routes are not actually used for packet forwarding by the originator of the
aggregate route, but only by the receiver (if it wishes). Instead of requiring a route-peer
6 - 6 SSR User Reference Manual
Page 79
to know about in dividual subnets which would increas e the size of its ro uting table, the
peer is only informed about an aggregate-route which contains all the subnets.
Like export policies, aggregate-routes can have up to three components:
• Aggregate-Destination
• Aggregate-Source
• Route-Filter
Aggregate-Destination
This component specifies the aggregate/summarized route. It also specifies the
attributes associated with the aggregate route. The preference to be associated with an
aggregate route can be specified using this component.
Aggregate-Source
This component specifies the source of the routes contributing to an aggregate/
summarized route. It can also specify the preference to be associated with the
contributing routes from this source. This preference can be overridden by explicitly
specifying a preference with the route-filter.
Chapter 6: Routing Policy Configuration Guide
Route-Filter
The routes contributing to an aggregate can be identified by their associated attributes:
• Protocol type (RIP, OSPF, BGP, Static, Direct, Aggregate).
• Autonomous system from which the route was learned.
• AS path associated with a route. When BGP is configured, all routes are assigned an
AS path when they are added to the routing table. For interi or routes, this AS path
specifies IGP as the origin and no ASs in the AS path ( the current AS is added when
the route is exported). For BGP routes, the AS path is stored as learned from BGP.
• Tag associated with a route. Both OSPF and RIP version 2 currently support tags.
All other protocols have a tag of zero.
In some cases, a combination of the associated attributes can be specified to identify
the routes contributing to an aggregate.
This component specifies the individual routes that are to be aggregated or
summarized. The preference to be associated with these routes can also be explicitly
specified using this component.
The contributing routes are ordered according to the aggregation preference that
applies to them. If there is more than one contributing route with the same aggreg ating
preference, the route's own preferences are used to order the routes. The preference of
the aggregate route will be that of contributing route with the lowest aggregate
preference.
SSR User Reference Manual 6 - 7
Page 80
Chapter 6: Routing Policy Configuration Guide
A route may only contribute to an aggregate route that is more general than itself; it
must match the aggregat e und er its mas k. Any g iven rou te may only con tribut e to one
aggregate route, which will be the most specific configured, but an aggregate route
may contribute to a more general aggregate.
An aggregate-route only comes into existence if at least one of its contributing routes
is active.
Authentication
Authentication guarantees that routing information is only imported from trusted
routers. Many protocols like RIP V2 and OSPF provide mechanisms for authenticating
protocol exchanges. A variety of authentication schemes can be used. Authentication
has two components – an Authentication Method and an Authentication Key. Many
protocols allow dif ferent authentication methods an d keys to be used in dif ferent parts
of the network.
Authentication Methods
There are mainly two authentication methods:
Simple Password: In this method, an authentication key of up to 8 characters is
included in the packet. If this does not match what is expected, the pack et is discarded.
This method provides little security, as it is possible to learn the authentication key by
watching the protocol packets.
MD5: This method uses the MD5 algorithm to create a crypto-checksum of the
protocol packet and an authentication key of up to 16 characters. The transmitted
packet does not contain the authentication key itself, instead it contains a cryptochecksum, called the digest. The receiving router performs a calculation using the
correct authentication key and discard the packet if the digest does not match. In
addition, a sequence number is maintained to pr event the replay of older packets. This
method provides a much strong er a ssurance that routing data originated from a router
with a valid authentication key.
Many protocols allow the specification of two authentication keys per interface.
Packets are always sent using the primary keys, b ut received packets are checked with
both the primary and secondary keys before being discarded.
Authentication Keys and Key Management
An authentication key permits generation and verification of the authentication field in
protocol packets. In many situations, the same primary and secondary key s are used on
several interfaces of a router. For ease of man agement of keys, a concept of key-chain
is introduced. Each key-chain has an identifier and contains up to two keys. One of
keys is the primary key and other is the secondary key. Outgoing packets use the
primary authentication key, but incoming packets may match either the primary or
6 - 8 SSR User Reference Manual
Page 81
Chapter 6: Routing Policy Configuration Guide
secondary authentication key. In the router configuration mode, instead of specifying
the key for each interface (which can be up to 16 characters long), a key-chain
identifier is specified.
Configure Simple Routing Policies
Simple routing policies provide an efficient way for routing information to be
exchanged between routing protocols. The redistribute command can be used to
redistribute routes from one routing domain into another routing domain.
Redistribution of routes between routing domains is based on route policies. A route
policy is a set of conditions based on which routes are redistributed. While the
redistribute command is expected to satisfy the export policy requirement for most
users, complex export policies may require the use of the commands listed under
Export Policies.
The general syntax of the redistribute command is as follows:
ip-router policy redistribute from-proto
[network
<number>
<ipAddr-mask>
|restrict] [source-as
[exact|refines|between
<number>
The from-proto parameter specifies the protocol of the source routes. The values for
the from-proto parameter are rip, o spf, bgp, direct, static, aggr egate and ospf- ase. The
to-proto parameter specifies the destination protocol where the routes are to be
exported. The values for the to-proto parameter are rip, ospf and bgp. The network
parameter provides a means to define a filter for the routes to be distributed. The
network parameter defines a filter that is made up of an IP ad dress and a mas k. Routes
that match the filter are considered as eligible for redistribution.
Every protocol (RIP, OSPF, and BGP) has a configurable parameter that specifies
default-metric associated with routes exported to that protocol. If a metric is not
explicitly specified with the redistribute command, then it is inherited from the defaultmetric associated with the protocol to which the routes are being exported.
Redistributing Static Routes
Static routes may be redist ributed to anot her rou ting pro tocol s uch as R IP o r OSP F by
the following command. The network parameter specifies the set of static routes that
will be redistributed by this command. If all static routes are to be redistributed set the
network parameter to all. Note that the network parameter is a filter that is used to
specify routes that are to be redistributed.
<protocol>
] [target-as
to-proto
<low-high>
<number>
<protocol>
]] [metric
]
SSR User Reference Manual 6 - 9
Page 82
Chapter 6: Routing Policy Configuration Guide
T o redistr ibut e stati c rout es, enter one of the fol lowing commands i n Conf igure mode:
To redistribute static routes into RIP. ip-router policy redistribute from-
proto static to-proto rip network all
To redistribute static routes into OSPF. ip-router policy redistribute from-
proto static to-proto ospf network all
Redistributing Directly Attached Networks
Routes to directly attached networks are redistribu ted to an other ro uting pr otocol such
as RIP or OSPF by the following command. The network parameter specifies a set of
routes that will be redistributed by this command. If all direct routes are to be
redistributed set the network parameter to all. Note that the network parameter is a
filter that is used to specify routes that are to be redistrib uted.
T o redi stribute di rect rout es, enter one of the followin g commands i n Config ure mode:
To redistribute direct routes into RIP. ip-router policy redistribute from-
proto direct to-proto rip network all
To redistribute direct routes into OSPF. ip-router policy redistribute from-
proto direct to-proto ospf network all
Redistributing RIP into RIP
The SSR routing process requires RIP redistribution into RIP if a protocol is
redistributed into RIP.
To redistribute RIP into RIP, enter the following command in Configure mode:
To redistribute RIP into RIP. ip-router policy redistribute from-
proto rip to-proto rip
Redistributing RIP into OSPF
RIP routes may be redistributed to OSPF.
To redistribute RIP into OSPF, enter the following command in Configure mode:
To redistribute RIP into OSPF. ip-router policy redistribute from-
proto rip to-proto ospf
6 - 10 SSR User Reference Manual
Page 83
Chapter 6: Routing Policy Configuration Guide
Redistributing OSPF to RIP
For the purposes of route redistribution and import-export policies, OSPF intra- and
inter-area routes are referred to as ospf routes, and external routes redistributed into
OSPF are referred to as ospf-ase routes. Examples of ospf-ase routes include static
routes, rip routes, direct routes, bgp routes, or aggregate routes, which are
redistributed into an OSPF domain.
OSPF routes may be redistributed into RIP. To redistribute OSPF into RIP, enter the
following command in Configure mode:
To redistribute ospf-ase routes into rip. ip-router policy redistribute from-
proto ospf-ase to-proto rip
To redistribute ospf routes into rip. ip-router policy redistribute from-
proto ospf to-proto rip
Redistributing Aggregate Routes
The aggregate parameter causes an aggregate route with the specified I P addr ess and
subnet mask to be redistributed.
Note:
To redistribute aggregate routes, enter one of the following commands in Configure
mode:
To redistribute aggregate routes into
RIP.
To redistribute aggregate routes into
OSPF.
The aggregate route must first be created using the aggr-gen command.
This command creates a specified aggregate route for routes that match the
aggregate.
ip-router policy redistribute fromproto aggregate to-proto rip
ip-router policy redistribute fromproto aggregate to-proto OSPF
Simple Route Redistribution Examples
Example 1: Redistribution into RIP
For all examples gi ven in this s ection, ref er to the configur ations shown in Figure 2 on
page 6 - 21.
The following configuration commands for router R1:
• Determine the IP address for each interface
SSR User Reference Manual 6 - 11
Page 84
Chapter 6: Routing Policy Configuration Guide
• Specify the static routes configured on the router
• Determine its RIP configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 160.1.1.1/16 port et.1.6
interface create ip to-r7 address-netmask 170.1.1.1/16 port et.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure a default route through 170.1.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route default gateway 170.1.1.7
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure static routes to the 135.3.0.0 subnets reachable through
! R3.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 135.3.1.0/24 gateway 130.1.1.3
ip add route 135.3.2.0/24 gateway 130.1.1.3
ip add route 135.3.3.0/24 gateway 130.1.1.3
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.190.1.2
ip add route 160.1.5.0/24 gateway 120.190.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip start
rip set default-metric 2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Interface Configuration. Create a RIP interfaces, and set
! their type to (version II, multicast).
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip add interface to-r41
rip add interface to-r42
rip add interface to-r6
rip set interface to-r41 version 2 type multicast
rip set interface to-r42 version 2 type multicast
rip set interface to-r6 version 2 type multicast
6 - 12 SSR User Reference Manual
Page 85
Chapter 6: Routing Policy Configuration Guide
Exporting a given static route to all RIP interfaces
Router R1 has several stat ic ro utes of which on e is the def ault ro ute. We would export
this default route over all RIP interfaces.
ip-router policy redistribute from-proto static to-proto rip network default
Exporting all static routes to all RIP interfaces
Router R1 has several static routes. We would export these routes over all RIP
interfaces.
ip-router policy redistribute from-proto static to-proto rip network all
Exporting all static routes except the default route to all RIP interfaces
Router R1 has several static routes. W e would export all these routes except the default
route to all RIP interfaces.
ip-router policy redistribute from-proto static to-proto rip network all
ip-router policy redistribute from-proto static to-proto r ip network d efault
restrict
Example 2: Redistribution into OSPF
For all examples gi ven in this s ection, ref er to the configur ations shown in Figure 3 on
page 6 - 25.
The following configuration commands for router R1:
• Determine the IP address for each interface
• Specify the static routes configured on the router
• Determine its OSPF configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 140.1.3.1/24 port et.1.6
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.1.1.2
ip add route 160.1.5.0/24 gateway 120.1.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf start
SSR User Reference Manual 6 - 13
Page 86
Chapter 6: Routing Policy Configuration Guide
ospf create area 140.1.0.0
ospf create area backbone
ospf set ase-defaults cost 4
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Interface Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf add interface 140.1.1.1 to-area 140.1.0.0
ospf add interface 140.1.2.1 to-area 140.1.0.0
ospf add interface 140.1.3.1 to-area 140.1.0.0
ospf add interface 130.1.1.1 to-area backbone
Exporting all interface and static routes to OSPF.
Router R1 has several stati c rout es. We would like to export all these static routes and
direct-routes (routes to connected networks) into OSPF.
ip-router policy redistribute from-proto static to-proto ospf
ip-router policy redistribute from-proto direct to-proto ospf
Note:
The network parameter specifying the network-filter is opti onal. The
default value for this parameter is all, indicating all networks. Since in the
above example, we would like to export all static and direct routes into
OSPF, we have not specified this parameter.
Export all RIP, interface, and static routes to OSPF.
Note:
Also export interface, static, RIP, OSPF, and OSPF-ASE routes into RIP.
In the configur ation sho wn in Fig ure 3 on p age 6 - 25, suppos e if we decide to run R IP
Version 2 on network 120.190.0.0/16, connecting routers R1 and R2.
Router R1 would like to export all RIP, interface, and static routes to OSPF.
ip-router policy redistribute from-proto rip to-proto ospf
ip-router policy redistribute from-proto direct to-proto ospf
ip-router policy redistribute from-proto static to-proto ospf
Router R1 would also like to export interface, static, RIP, OSPF, and OSPF-ASE routes
into RIP.
ip-router policy redistribute from-proto direct to-proto rip
ip-router policy redistribute from-proto static to-proto rip
ip-router policy redistribute from-proto rip to-proto rip
ip-router policy redistribute from-proto ospf to-proto rip
ip-router policy redistribute from-proto ospf-ase to-proto rip
6 - 14 SSR User Reference Manual
Page 87
Chapter 6: Routing Policy Configuration Guide
Configure Advanced Routing Policies
Advanced Routing Policies are used for creating complex import/export policies that
cannot be done using the redistribute command. Advanced export policies provide
granular control over the targets where the routes are exported, the source of the
exported routes, and the individual routes which are exported. It provides the
capability to send different routes to the various route-peers. They can be u sed to
provide the same route with different attributes to the various route-peers.
Import policies control the importation of routes from routing protocols and their
installation in the routing database (Routing Information Base and Forwarding
Information Base). Import policies determine which routes received from other
systems are used by the SSR routing process. Us ing import policies, it is possible to
ignore route updates from an unreliable peer and give better preference to routes
learned from a trusted peer.
Export Policies
Advanced export policies can be constructed from one or more of the following
building blocks:
• Export Destinations - This component specifies the destination where the routes are
to be exported. It also specifies the attributes associated with the exported routes.
The interface, gateway or the autonomous system to which the routes are to be
redistributed are a few examples of export-destinations. The metric, type, tag, and
AS-Path are a few examples of attributes associated with the exported routes.
• Export Sources - This component specifies the source of the exported routes. It can
also specify the metric to be associated with the routes exported from this source.
The routes to be exported can be identified by their associated attributes, such as
protocol type, interface or the gateway from wh ich the route was received, and so on.
• Route Filter - This component provides the means to define a filter for the routes to
be distributed. Routes that match a filter are considered as eligible for redistribution.
This can be done using one of two methods:
• Creating a route-filter and associating an identifier with it. A route-filter has several network specifications associated with it. Every route is checked against the
set of network specifications associated with all route-filters to determine its eligibility for redistribution. The identifier associated with a route-filter is used in the
ip-router policy export command.
• Specifying the networks as needed in the ip-router policy export command.
If you want to create a complex ro ute-filter, and yo u intend to use that route-f ilter in
several export policies, then the first method is recommended. It you do not have
SSR User Reference Manual 6 - 15
Page 88
Chapter 6: Routing Policy Configuration Guide
complex filter requirements, then use the second method.
After you create one or more building blocks, they are tied together by the iprouter
policy export command.
To create route export policies, enter the following command in Configure mode:
Create an export policy.
<exp-dest-id>
The
ip-router policy export destination
[source
<ipAddr-mask>
[metric
is the identifier of the export-destination wh ich determines
where the routes are to be exported. If no routes to a particular destination are to be
exported, then no additional parameters are required.
<exp-src-id>
The
, if specified, is the identifier of the export-source which
determines the source of the exported routes. If a export-policy for a given exportdestination has more than one export-source, then the ip-router policy export
destination <exp-dest-id> command should be repeated for each
<filter-id>
The
, if specified, is the identifer of the route-filter associated with this
export-policy. If there is more than one route-filter for any export-destination and
export-source combination, then the ip-r outer policy export destination <exp-dest-id>
source <exp-src-id> command should be repeated for each
Creating an Export Destination
T o create an export destination, en ter one the following commands in Co nfigure mode:
<exp-src-id>
[exact|refines|between
<number>
|restrict]]]]
[filter
<exp-dest-id>
<filter-id>
<low-high>
<exp-src-id>
<filter-id>
|[network
]
.
.
Create a RIP export destination.
Create an OSPF export destination.
6 - 16 SSR User Reference Manual
ip-router policy create rip-export-
<
destination
name>
ip-router policy create ospf-export-
<
destination
name>
Page 89
Chapter 6: Routing Policy Configuration Guide
Creating an Export Source
To create an export source, enter one of the following commands in Configure mode:
Create a RIP export source. ip-router policy create rip-export-
source <
name>
Create an OSPF export source. ip-router policy create ospf-export-
source <
name>
Import Policies
Import policies can be co nstr ucted fr om on e or more of t he followin g buildi ng block s:
• Import-source - This component specifies the source of the imported routes. It can
also specify the preference to be associated with the routes imported from this
source. The routes to be imported can be identified by their associated attributes,
including source protocol, Source interface or gateway from which the route was
received, and so on.
• Route Filter - This component provides the means to define a filter for the routes to
be imported. Routes that match a filter are considered as eligible for im portation.
This can be done using one of two methods:
• Creating a route-filter and associating an identifier with it. A route-filter has sev-
eral network specifications associated with it. Every route is checked against the
set of network specifications associated with all route-filters to determine its eligibility for importation. The identifier associated with a route-filter is used in the
ip-router policy import command.
• Specifying the networks as needed in the ip-router policy import command.
If you want to create a complex ro ute-filter, and yo u intend to use that route-f ilter in
several import policies, then the first method is recommended. It you do not have
complex filter requirements, then use the second method.
After you create one or more building blocks, they are tied together by the iprouter
policy import command.
To create route import policies, enter the following command in Configure mode:
Create an import policy.
ip-router policy import source
<filter-id>
[exact|refines|between
<number>
|[network
|restrict]]]
<ipAddr-mask>
<low-high>
<imp-src-id>
] [preference
[filter
SSR User Reference Manual 6 - 17
Page 90
Chapter 6: Routing Policy Configuration Guide
<imp-src-id>
The
of the imported routes. If no r outes from a part icular source are to be imp orted, then no
additional parameters are required.
<filter-id>
The
import-policy. If there is more than one route-filter for any import-source, then the ip-
router policy import source <imp-src-id> command should be repeated for each
<filter-id>
is the identifier of the import-source that determines the source
, if specified, is the identifer of the route-filter associated with this
.
Creating an Import Source
Import sources specify the routing protocol from which the routes are imported. The
source may be RIP or OSPF.
To create an import source, enter one of the following commands in Configure mode:
Create a RIP import destination. ip-router policy create rip-import-
source <
Create an OSPF import destination. ip-router policy create ospf-import-
source <
name>
name>
Creating a Route Filter
Route policies are defined by specifying a set of filters that will match a certain route
by destination, or by destination and mask.
To create route filters, enter the following command in Configure mode:
Create a route filter. ip-router policy create filter <
network
id>
<IP-address/mask>
Creating an Aggregate Route
Route aggregation is a method of generating a more general route, given the presence
of a specific route. The routing process does not perform any aggregation unless
explicitly requested. Aggregate-routes can be constructed from one or more of the
following building blocks:
• Aggregate-Destination - This component specifies the aggregate/summarized route.
It also specifies the attributes associated with the aggregate route. The preference to
be associated with an aggregate route can be specified using this component.
• Aggregate-Source - This component specifies the source of the routes contributing
to an aggregate/summarized route. It can also specif y the preference to be associated
name-
6 - 18 SSR User Reference Manual
Page 91
Chapter 6: Routing Policy Configuration Guide
with the contributing routes from this source. The routes contributing to an
aggregate can be identified by their associated attributes, including protocol type,
tag associated with a route, and so on.
• Route Filter - This component provides the means to define a filter for the routes to
be aggregated or summarized. Routes that match a filter are considered as eligible
for aggregation. This can be done using one of two methods:
• Creating a route-filter and associating an identifier with it. A route-filter has sev-
eral network specifications associated with it. Every route is checked against the
set of network specifications associated with all route-filters to determine its eligibility for aggregation. The identifier associated with a route-filter is used in the
ip-router policy aggr-gen command.
• Specifying the networks as needed in the ip-router policy aggr-gen command.
If you want to create a complex ro ute-filter, and yo u intend to use that route-f ilter in
several aggregates, then the first method is recommended. It you do not have
complex filter requirements, then use the second method.
After you create one or more building blocks, they are tied together by the iprouter
policy aggr-gen command.
To create aggregates, enter the following command in Configure mode:
Create an aggregate
route.
The
aggregate/summarized route.
The
aggregate route. If an aggregate has more than one aggregate-sour ce, then the ip-router
policy aggr-gen destinati on <aggr -dest-id> command should be repeated for each
<aggr-src-id>
The
there is more than one route-filter for a ny aggreg ate-destination and agg regate-source
combination, then the ip-router policy aggr-gen destination <aggr-dest-id> source
<aggr-src-id> command should be repeated for each
ip-router policy aggr-gen destination
[source
id>
|[network
[exact|refines|between
<number>
<aggr-dest-id>
<aggr-src-id>
is the identifier of the aggregate-source that contributes to an
.
<filter-id>
is the identifer of the route-filter associated with this aggregate. I f
<aggr-src-id>
<ipAddr-mask>
|restrict]]]]
[filter
<low-high>
<aggr-dest-id>
<filter-
] [preference
is the identifier of the aggregate-destination that specifies the
<filter-id>
.
SSR User Reference Manual 6 - 19
Page 92
Chapter 6: Routing Policy Configuration Guide
Creating an Aggregate Destination
To create an aggregate destination, enter the following command in Configure mode:
Create an aggregate destination. ip-router policy create aggr-gen-dest
name>
<
network <
ipAddr-mask
>
Creating an Aggregate Source
To create an aggregate source, enter the following command in Configure mode:
Create an aggregate source. ip-router policy create aggr-gen-
source <
name>
protocol
<protocol-name>
Examples of Import Policies
Example 1: Importing from RIP
The importation of RIP routes may be controlled by any o f protocol, sour ce interface,
or source gateway . If more than one is specified, they are processed from most gener al
(protocol) to most specific (gateway).
RIP does not support the use of preference to choose between routes of the same
protocol. That is left to the protocol metrics.
For all examples in this section, refer to the configuration shown in Figure 2 on page
6 - 21.
6 - 20 SSR User Reference Manual
Page 93
SSR User Reference Manual 6 - 21
Figure 2: Exporting to RIP
Internet
R41
R1
R2
R3
R7
135.3.1.1/24
135.3.2.1/24
135.3.3.1/24
140.1.1.4/24
140.1.1.1/24
130.1.1.1/16
130.1.1.3/16
120.190.1.1/16
120.190.1.2/16
202.1.0.0/10
160.1.5.0/24
160.1.1.1/16
140.1.2.1/24
170.1.1.1/16
d
e
fa
u
l
t
170.1.1.7/16
RIP V2
RIP v2
(RIP V1)
10.51.0.0/16
Page 94
Chapter 6: Routing Policy Configuration Guide
The following configuration commands for router R1
• Determine the IP address for each interface.
• Specify the static routes configured on the router.
• Determine its RIP configuration.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 160.1.1.1/16 port et.1.6
interface create ip to-r7 address-netmask 170.1.1.1/16 port et.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure a default route through 170.1.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route default gateway 170.1.1.7
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the 135.3.0.0 subnets reachable through
! R3.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 135.3.1.0/24 gateway 130.1.1.3
ip add route 135.3.2.0/24 gateway 130.1.1.3
ip add route 135.3.3.0/24 gateway 130.1.1.3
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.190.1.2
ip add route 160.1.5.0/24 gateway 120.190.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip start
rip set default-metric 2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Interface Configuration. Create a RIP interfaces, and set
! their type to (version II, multicast).
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip add interface to-r41
rip add interface to-r42
rip add interface to-r6
rip set interface to-r41 version 2 type multicast
6 - 22 SSR User Reference Manual
Page 95
Chapter 6: Routing Policy Configuration Guide
rip set interface to-r42 version 2 type multicast
rip set interface to-r6 version 2 type multicast
Importing a selected subset of routes from one of the RIP trusted gateways.
Router R1 has several RIP peers. Router R41 has an interface on the network
10.51.0.0. By default, router R41 advertises network 10.51.0.0/16 in its RIP updates.
Router R1 would like to import all routes except the 10.51.0.0/16 route from its peer
R41.
1. Add the peer 140.1.1.41 to the list of trusted an d source gateway s.
rip add source-gateways 140.1.1.41
rip add trusted-gateways 140.1.1.41
2. Create a RIP import source with the gateway as 140.1.1.4 since we would like to
import all routes except the 10.51.0.0/16 route from this gateway.
ip-router policy create rip-import-source ripImpSrc144 gateway 140.1.1.4
3. Create the Import-Policy, impor ting all routes excep t the 10.51.0. 0/16 route fro m
gateway 140.1.1.4
ip-router policy import source ripImpSrc144 network all
ip-router policy import source ripImpSrc144 network 10.51.0.0/16 restrict
Importing a selected subset of routes from all RIP peers accessible over a certain interface.
Router R1 has several RIP peers. Router R41 has an interface on the network
10.51.0.0. By default, router R41 advertises network 10.51.0.0/16 in its RIP updates.
Router R1 would like to import al l routes except the 10.51.0.0/16 route from all its peer
which are accessible over interface 140.1.1.1.
1. Create a RIP import source with the interface as 140.1.1.1 , since we would like to
import all routes except the 10.51.0.0/16 route from this interface.
ip-router policy create rip-import-source ripImpSrc140 interface 140.1.1.1
2. Create the Import-Policy importing all routes except the 10.51.0.0/16 route from
interface 140.1.1.1
ip-router policy import source ripImpSrc140 network all
ip-router policy import source ripImpSrc140 network 10.51.0.0/16 restrict
Example 2: Importing from OSPF
Due to the nature of OSPF, only the importation of ASE routes may be controlled.
OSPF intra-and inter-area routes are always imported into the SSR routing table with
a preference of 10. If a tag is specified, the import clause will only apply to routes with
the specified tag.
SSR User Reference Manual 6 - 23
Page 96
Chapter 6: Routing Policy Configuration Guide
It is only possible to restrict the importation of OSPF ASE routes when functioning as
an AS border router.
Like the other interior protocols, preference cannot be used to choose between OSPF
ASE routes. That is done by the OSPF costs. Routes that are rejected by policy are
stored in the table with a negative preference.
For all examples in this section, refer to the configuration shown in Figure 3 on page
6 - 25.
6 - 24 SSR User Reference Manual
Page 97
SSR User Reference Manual 6 - 25
Figure 3: Exporting to OSPF
BGP
R1
R2
R3
R41
A r e a B a c k b o n e
A r e a 140.1.0.0
(RIP V2)
140.1.1.1 /24
140.1.2.1/24
140.1.5/24
190.1.1.1/16
120.190.1.1/16
160.1.5.2/24
R10
R5 R7
202.1.2.2/16
140.1.3.1/24
130.1.1.1/16
R8
A r e a 150.20.0.0
150.20.3.1/16
150.20.3.2/16
140.1.1.2/24
130.1.1.3/16
120.190.1.2/16
160.1.5.2/24
Page 98
Chapter 6: Routing Policy Configuration Guide
The following configuration commands for router R1:
• Determine the IP address for each interface
• Specify the static routes configured on the router
• Determine its OSPF configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 140.1.3.1/24 port et.1.6
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.1.1.2
ip add route 160.1.5.0/24 gateway 120.1.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf start
ospf create area 140.1.0.0
ospf create area backbone
ospf set ase-defaults cost 4
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! OSPF Interface Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ospf add interface 140.1.1.1 to-area 140.1.0.0
ospf add interface 140.1.2.1 to-area 140.1.0.0
ospf add interface 140.1.3.1 to-area 140.1.0.0
ospf add interface 130.1.1.1 to-area backbone
Importing a selected subset of OSPF-ASE routes.
1. Create a OSPF import source so that only routes that have a tag of 100 are considered for importation.
ip-router policy create ospf-import-source ospfImpSrct100 tag 100
2. Create the Import-Policy importing all OSPF ASE routes with a tag of 100 except
the default ASE route.
ip-router policy import source ospfImpSrct100 network all
ip-router policy import source ospfImpSrct100 network default restrict
6 - 26 SSR User Reference Manual
Page 99
Examples of Export Policies
Example 1: Exporting to RIP
Exporting to RIP is controlled by any of protocol, interface or gateway. If more than
one is specified, they are processed from most general (protocol) to most specific
(gateway).
It is not possible to set metrics for exporting RIP routes into RIP. Attempts to do this
are silently ignored.
If no export policy is specified, RIP and interface routes are exported into RIP. If any
policy is specified, the defaults are overridden; it is necessary to explicitly specify
everything that should be exported.
RIP version 1 assumes that all subnets of the shared network have the same subnet
mask so it is only able to propagate subnets of that network. RIP version 2 removes
that restriction, and is capable of propagating all routes when not sending version 1
compatible updates.
To announce routes which specify a next h op of the lo op back in terface ( i. e. static an d
internally generated default routes) via RIP, it is necessary to specify the metric at some
level in the export policy. Just setting a default metric for RIP is not sufficient. This is
a safeguard to verify that the announcement is intended.
Chapter 6: Routing Policy Configuration Guide
For all examples in this section, refer to the configuration shown in Figure 2 on page
6 - 21.
The following configuration commands for router R1:
• Determine the IP address for each interface
• Specify the static routes configured on the router
• Determine its RIP configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Create the various IP interfaces.
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
interface create ip to-r2 address-netmask 120.190.1.1/16 port et.1.2
interface create ip to-r3 address-netmask 130.1.1.1/16 port et.1.3
interface create ip to-r41 address-netmask 140.1.1.1/24 port et.1.4
interface create ip to-r42 address-netmask 140.1.2.1/24 port et.1.5
interface create ip to-r6 address-netmask 160.1.1.1/16 port et.1.6
interface create ip to-r7 address-netmask 170.1.1.1/16 port et.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure a default route through 170.1.1.7
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route default gateway 170.1.1.7
SSR User Reference Manual 6 - 27
Page 100
Chapter 6: Routing Policy Configuration Guide
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the 135.3.0.0 sub nets reachable through
! R3.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 135.3.1.0/24 gateway 130.1.1.3
ip add route 135.3.2.0/24 gateway 130.1.1.3
ip add route 135.3.3.0/24 gateway 130.1.1.3
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! Configure default routes to the other subnets reachable through R2.
!+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
ip add route 202.1.0.0/16 gateway 120.190.1.2
ip add route 160.1.5.0/24 gateway 120.190.1.2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Box Level Configuration
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip start
rip set default-metric 2
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
! RIP Interface Configuration. Create a RIP interfaces, and set
! their type to (version II, multicast).
!++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
rip add interface to-r41
rip add interface to-r42
rip add interface to-r6
rip set interface to-r41 version 2 type multicast
rip set interface to-r42 version 2 type multicast
rip set interface to-r6 version 2 type multicast
Exporting a given static route to all RIP interfaces
Router R1 has several static routes, of which one is th e default route. We would export
this default route over all RIP interfaces.
1. Create a RIP export destination since we would like to export routes into RIP.
ip-router policy create rip-export-destination ripExpDst
2. Create a Static export source since we would like to export static routes.
ip-router policy create static-export-source statExpSrc
As mentioned above, if no ex port po licy is specified, RIP and interface routes are
exported into RIP. If any policy is specified, the defaults are overridden; it is
necessary to explicitly specify everything that should be exported.
Since we would also like to export/redistribute RIP and direct routes into RIP , we
would also create export-sources for those protocols.
6 - 28 SSR User Reference Manual
 Loading...