

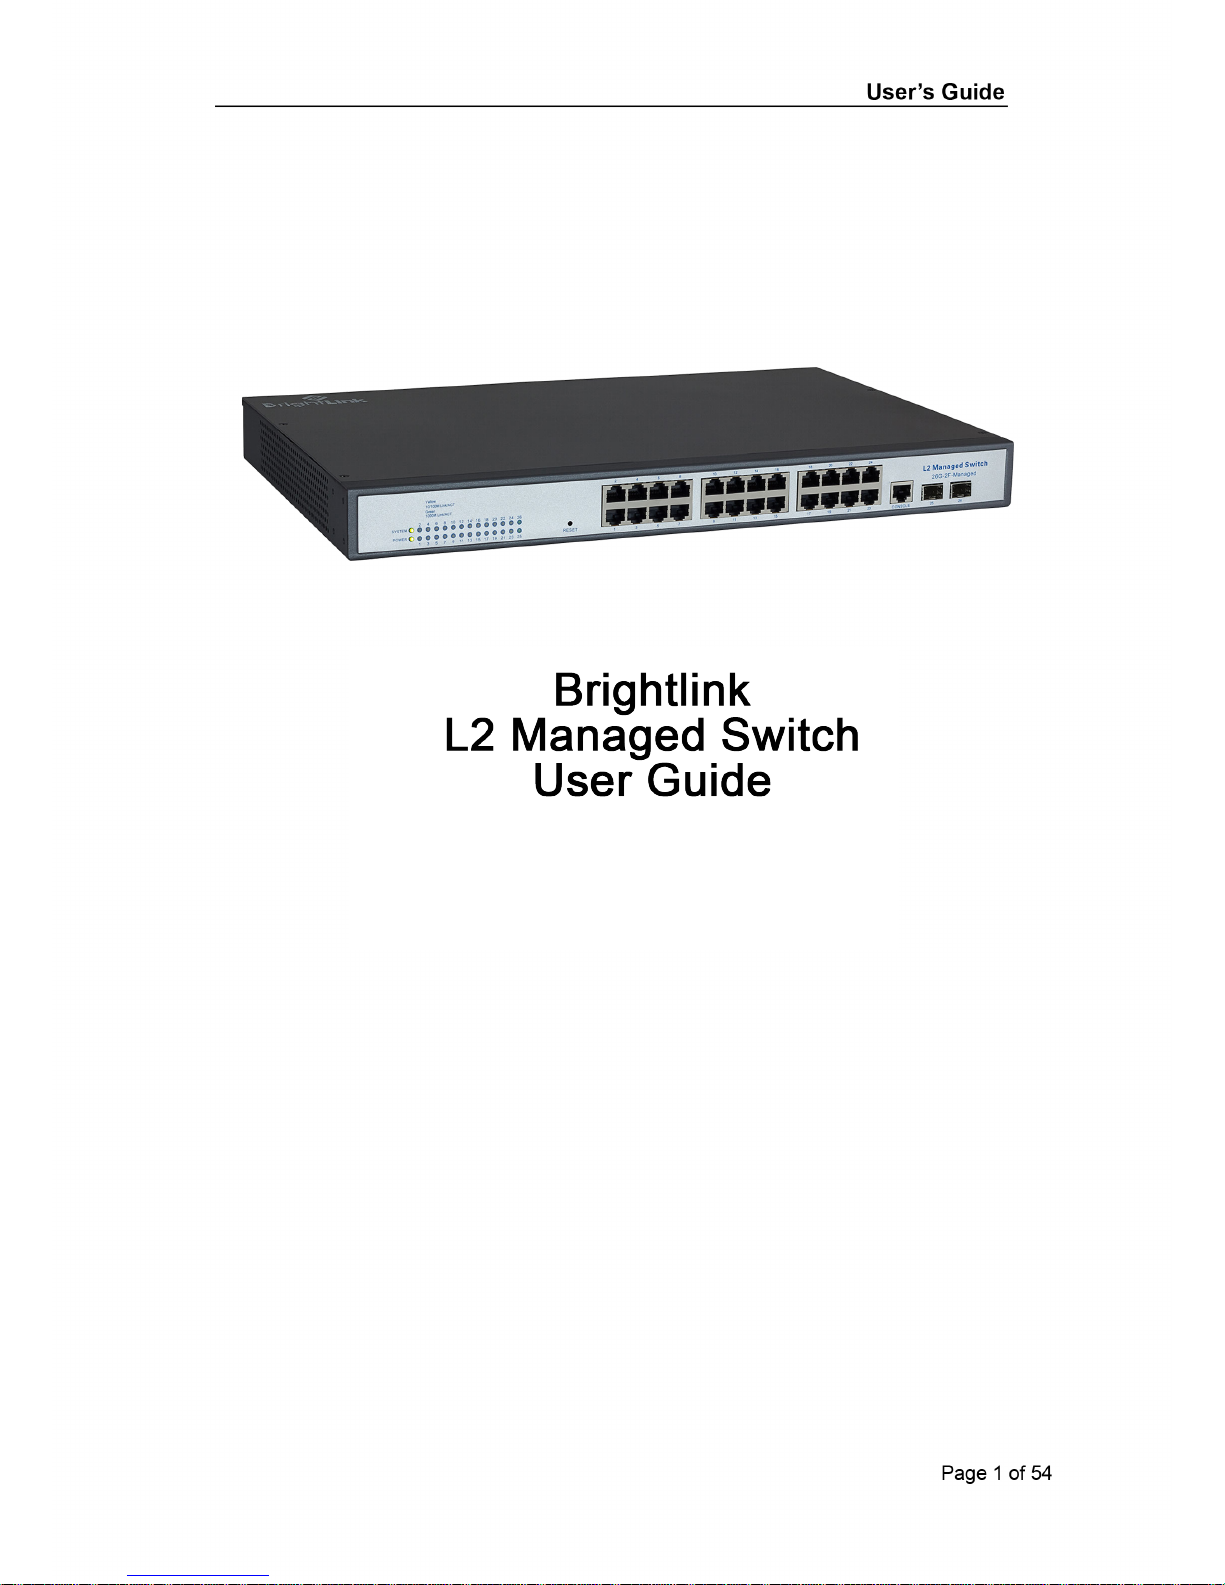
Page 1
Page 2
User’s Guide
Page 2 of 54
Contents
PART ONE HARDWARE INSTALLATION GUIDE ............................................................................... 5
CHAPTER 1 PRODUCT INSTRUCTION ......................................................................................................... 5
1.1 Introduction .................................................................................................................................. 5
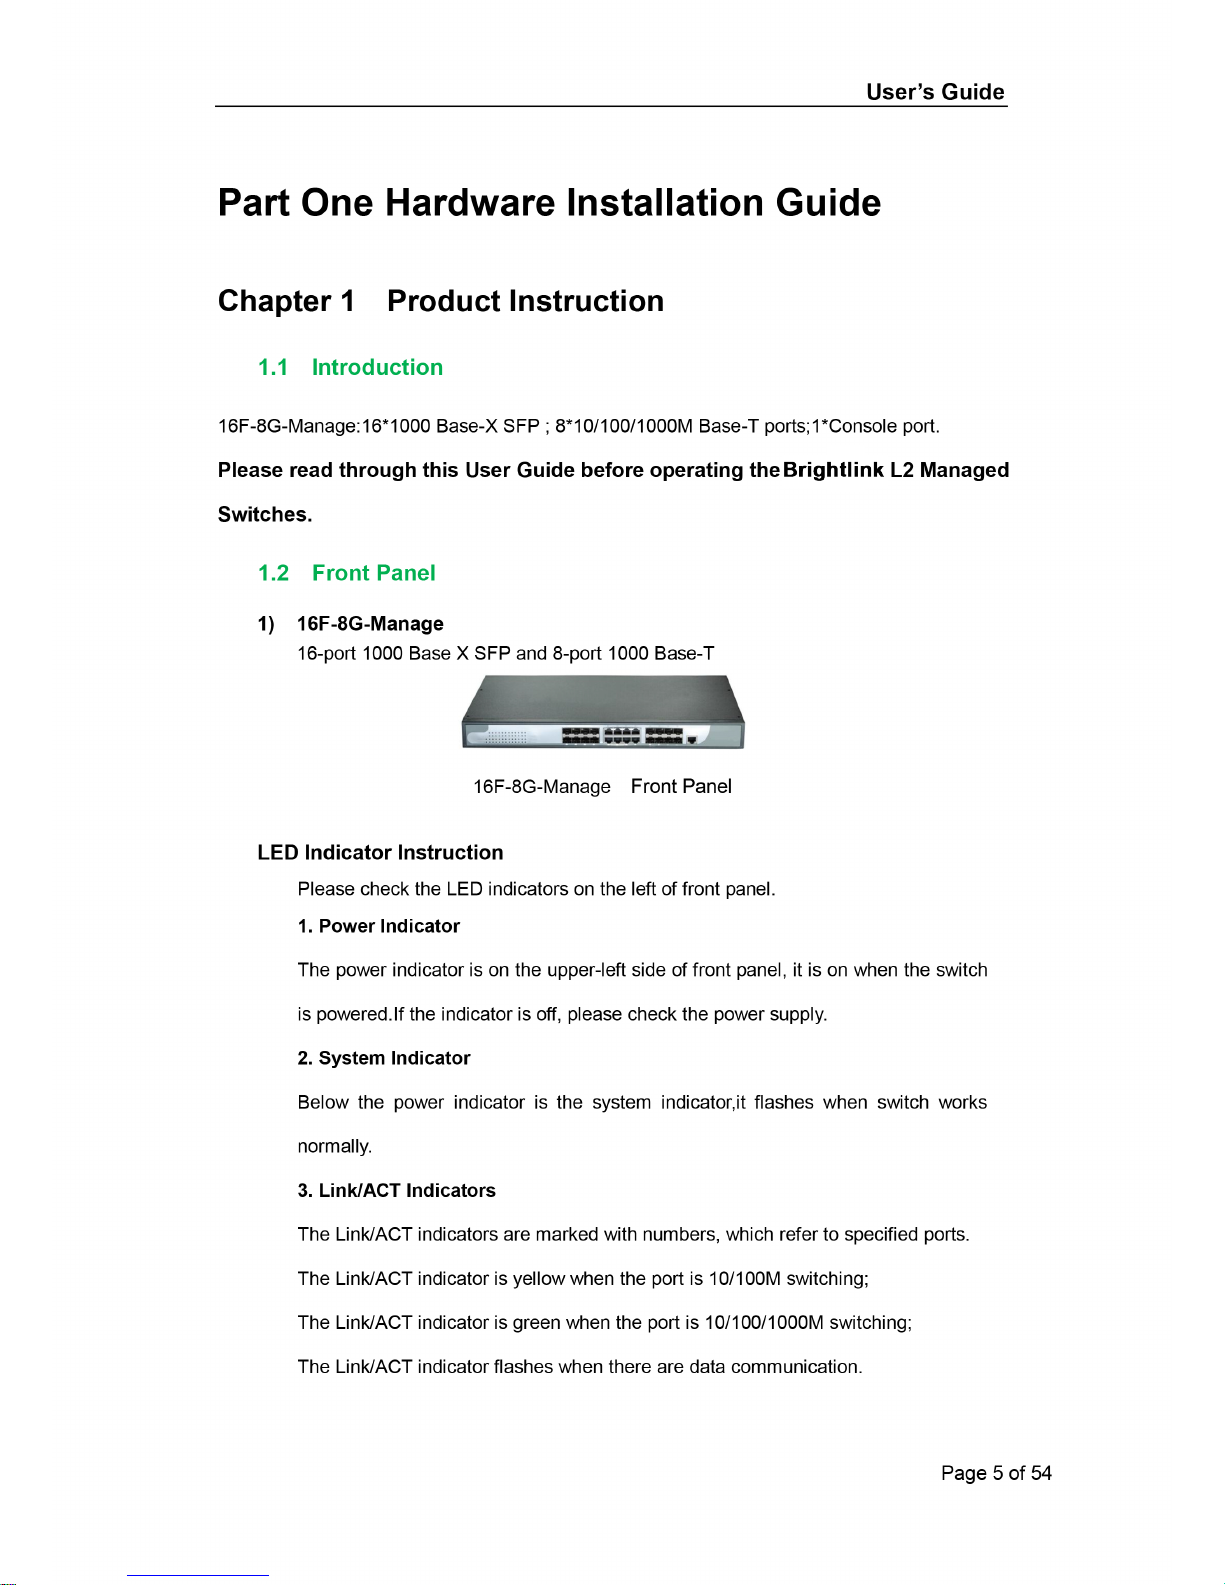
1.2 Front Panel .................................................................................................................................. 5
1.3 Rear Panel ...................................................................................................................................... 6
CHAPTER 2 PREPARATIONS BEFORE INSTRUCTION .................................................................................... 7
2.1 Precautions .................................................................................................................................. 7
2.2 Check Installation Environment ................................................................................................ 7
2.3 Installation Tools ......................................................................................................................... 7
CHAPTER 3 INSTALLATION ........................................................................................................................ 8
3.1 Install the Switch ......................................................................................................................... 8
3.2 Connect the power cord and grounded cord .......................................................................... 8
3.3 Test after Installation .................................................................................................................. 9
CHAPTER 4 TECHNICAL SPECIFICATIONS .............................................................................................. 10
4.1 Hardware Features: .................................................................................................................. 10
4.2 Software Features: ................................................................................................................... 10
PART TWO WEB CONFIGURATION GUIDE ...................................................................................... 12
CHAPTER 1 USER LOGIN ......................................................................................................................... 12
CHAPTER 2 DEVICE STATUS .................................................................................................................... 13
2.1 System Status ........................................................................................................................... 13
2.2 Port Statistics ............................................................................................................................. 14
2.3 LACP Statistics .......................................................................................................................... 14
2.4 RSTP Statistics ......................................................................................................................... 15
2.5 IGMP Statistics .......................................................................................................................... 15
Picture 2.5.1 IGMP Statistics ............................................................................................................ 15
Users can check the IGMP state statistics for current VLAN in this page. ................................ 15
CHAPTER 3 BASIC CONFIG ...................................................................................................................... 15
3.1 System Config ........................................................................................................................... 16
3.2 Port Config ................................................................................................................................. 16
3.3 Flow Control .............................................................................................................................. 17
CHAPTER 4 ADVANCED CONFIG .............................................................................................................. 17
4.1 IGMP Config .............................................................................................................................. 17
4.2 VLAN .......................................................................................................................................... 18
4.3 ARP Config ................................................................................................................................ 22
4.4 Link Aggregation ....................................................................................................................... 24
4.5 LACP Port Configuration ......................................................................................................... 25
4.6 LACP Port Configuration ......................................................................................................... 26
4.7 802.1X Configuration ............................................................................................................... 27
4.8 Port Mirroring Configuration .................................................................................................... 27
4.9 Qos Configuration ..................................................................................................................... 28
4.10 Storm Control .......................................................................................................................... 28
Page 3
User’s Guide
Page 3 of 54
4.11 PING ......................................................................................................................................... 29
CHAPTER 5 SYSTEM CONFIGURATION..................................................................................................... 29
5.1 Software Upgrade ..................................................................................................................... 29
5.2 Configuration Management ..................................................................................................... 30
5.3 System Warm Reset ................................................................................................................ 30
5.4 Factory Reset ............................................................................................................................ 30
PART THREE CLI CONFIGURATION GUIDE ........................................................................... 31
CHAPTER 2 CONSOLE PARAMETER CONFIGURATION .............................................................................. 35
CHAPTER 3 PORT CONFIGURATION ......................................................................................................... 36
CHAPTER 4 MAC CONFIGURATION ......................................................................................................... 37
CHAPTER 5 VLAN CONFIGURATION ....................................................................................................... 39
CHAPTER 6 ARP CONFIGURATION .......................................................................................................... 40
CHAPTER 7 LINK AGGREGATION CONFIGURATION ................................................................................. 41
CHAPTER 8 LACP CONFIGURATION ........................................................................................................ 42
CHAPTER 9 RSTP CONFIGURATION ........................................................................................................ 43
CHAPTER 10 USER GROUP CONFIGURATION ........................................................................................... 45
CHAPTER 11 QOS CONFIGURATION ........................................................................................................ 46
CHAPTER 12 PORT MIRROR CONFIGURATION ......................................................................................... 48
CHAPTER 13 IP ADDRESS CONFIGURATION ............................................................................................ 49
CHAPTER 14 DOT1X CONFIGURATION .................................................................................................... 51
CHAPTER 15 IGMP CONFIGURATION ...................................................................................................... 52
APPENDIX TROUBLE SHOOTING .................................................................................................... 54
Page 4
User’s Guide
Page 4 of 54
Packaging list:
Please open the product packaging box with care and check the following items:
L2 Managed Switch *1
Power Cord x1
DB9-RJ45 Cable
User Guide/CDx1
Installation accessories kit x1
If any of the above items are missing or damaged, please contact local reseller or
distributor for assistance.
Page 5
Page 6
User’s Guide
Page 6 of 54
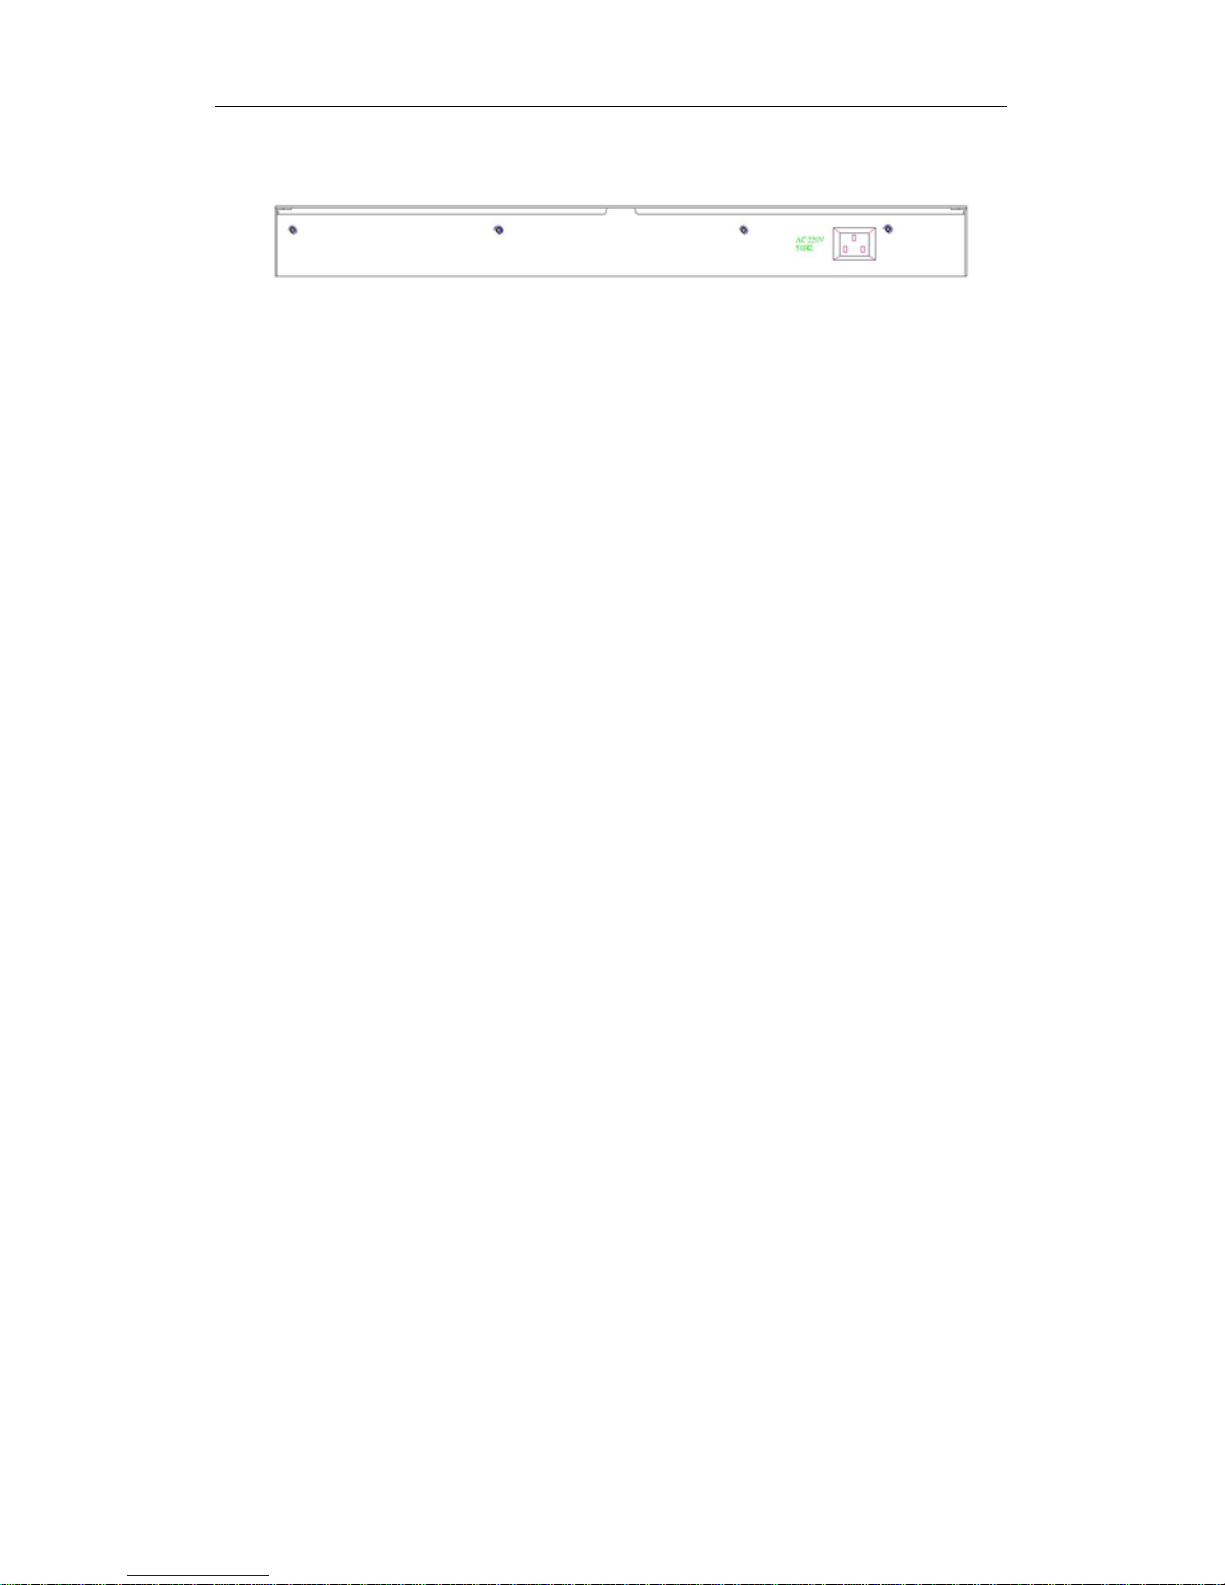
1.3 Rear Panel
Picture 1.3.1 Rear Panel
Power Socket: Three-core power socket is adopted,please connect female head of
power cord to the socket, and connect the AC power supply with male head.
Page 7
User’s Guide
Page 7 of 54
Chapter 2 Preparations before Instruction
2.1 Precautions
Please read the following precautions carefully before operation, to avoid damaging the
device or causing body injuries.
1). Please remove the power socket before cleaning the switch. Don’ wipe the switch
with wet cloth or wash the switch with liquid.
2). Don’t stock the device in damp environment or near water, to avoid water or moisture
penetrating into the inner device.
3). Don’t put the device on a unstable box or desk, the device will get damaged from
falling.
4). Please keep good ventilation indoor, and make sure the heat dissipation function of
switch works well.
5). The switch only works normally in suitable voltage. Please check the working voltage
first.
6). Please don’t open the switch enclosure randomly, especially when the switch is
powered on, there is risk of electric shock.
7). Please wear anti-static wrist strap when change the interface board,to avoid the
static electricity damage the board.
2.2 Check Installation Environment
The switch is for indoor use only, please pay attention to the following problems when
install the switch in a cabinet or put the device directly on the desktop.
1) The air vents of switch must have enough space to dissipate the heat inside
enclosure.
2) A good heat dissipation system in the cabinet or on the desktop.
3) The cabinet or desktop strong enough to support the weight of switch and
installation accessories.
4) Safe ground connection for the cabinet or desktop.
2.3 Installation Tools
1) Flathead screw driver
2) Cross screw driver
3) Anti-static wrist strap
Page 8
User’s Guide
Page 8 of 54
Chapter 3 Installation
3.1 Install the Switch
3.1.1 Install the switch on a 19 inch standard cabinet
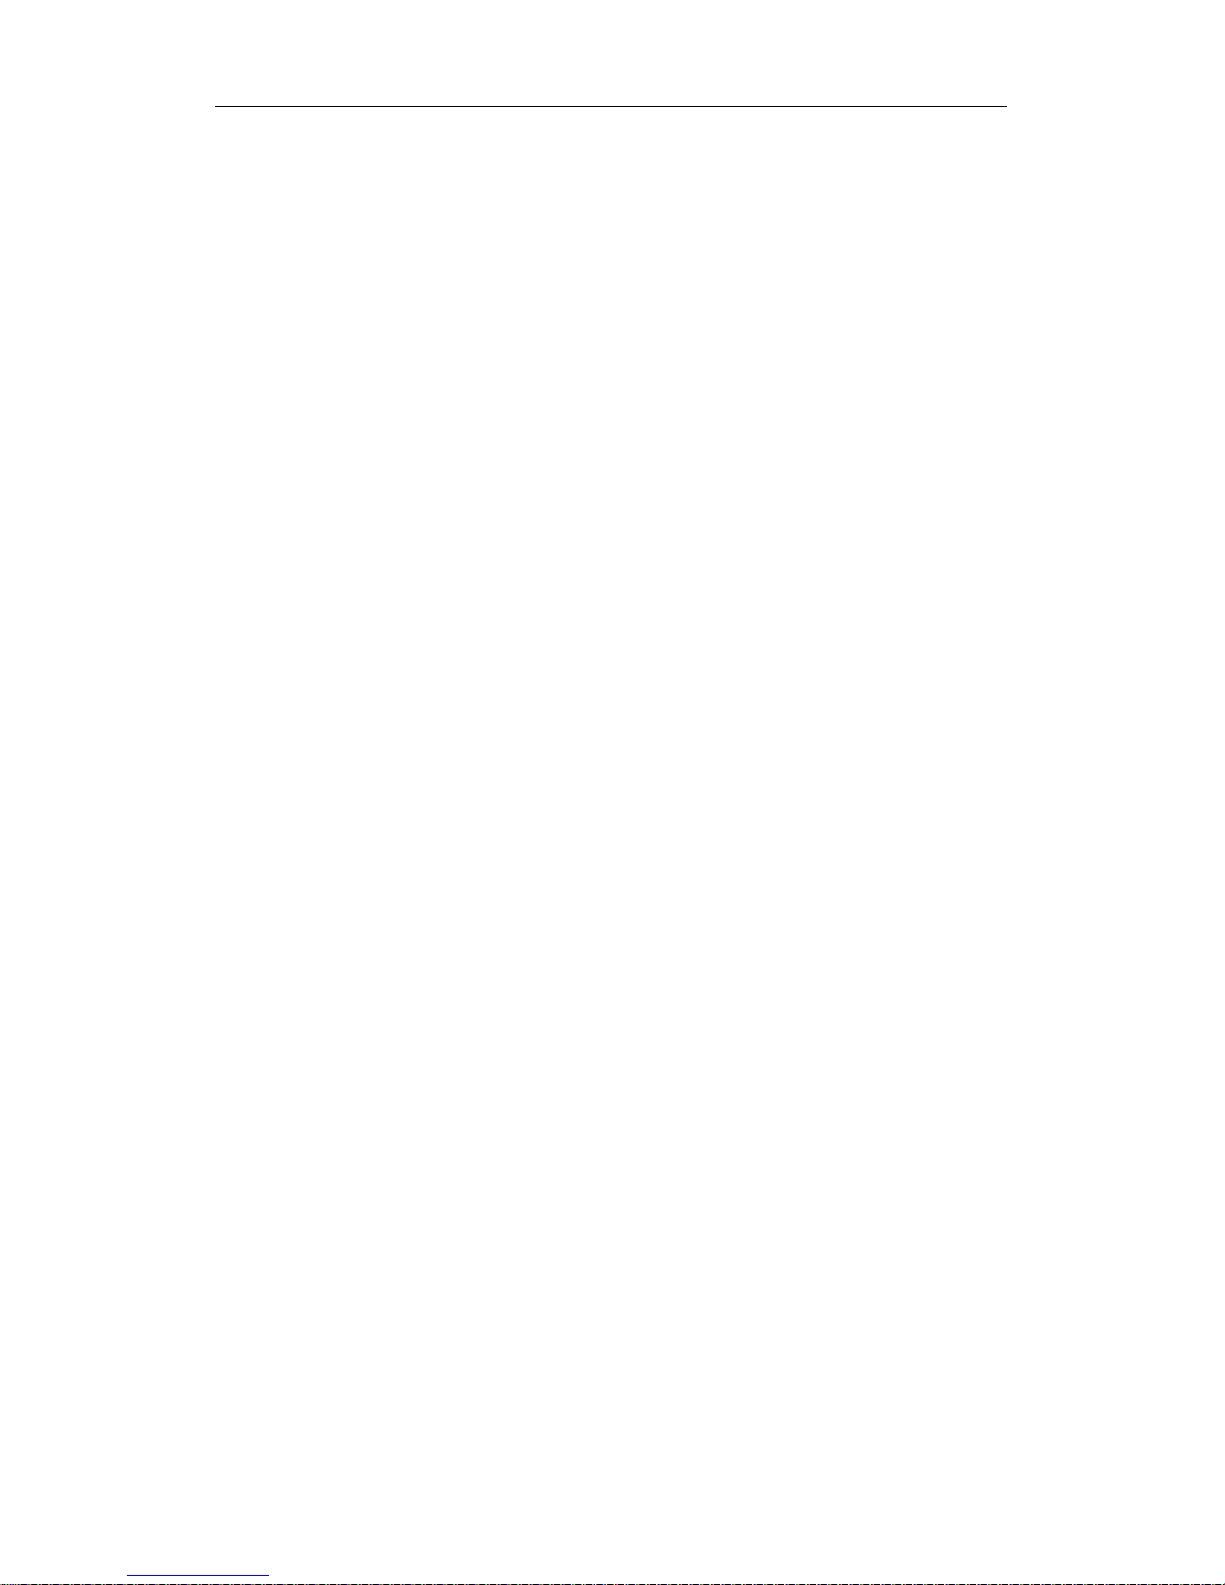
1) First fix the provided two L-shaped brackets on the two sides of switch.
2) Fix the switch on the rack with screws(screws are not provided).
Picture 3.1.1 Cabinet Installation
3.1.2 Install the switch on the desktop
When there is no 19 inch standard cabinet, the switch is usually put on clean
desktop. The operation is easier, please follow the below instructions:
1) Keep the desktop stable and safely grounded.
2) Set aside 10cm space around switch for heat dissipation.
3) Don’t put any heavy device on the switch.
3.2 Connect the power cord and grounded cord
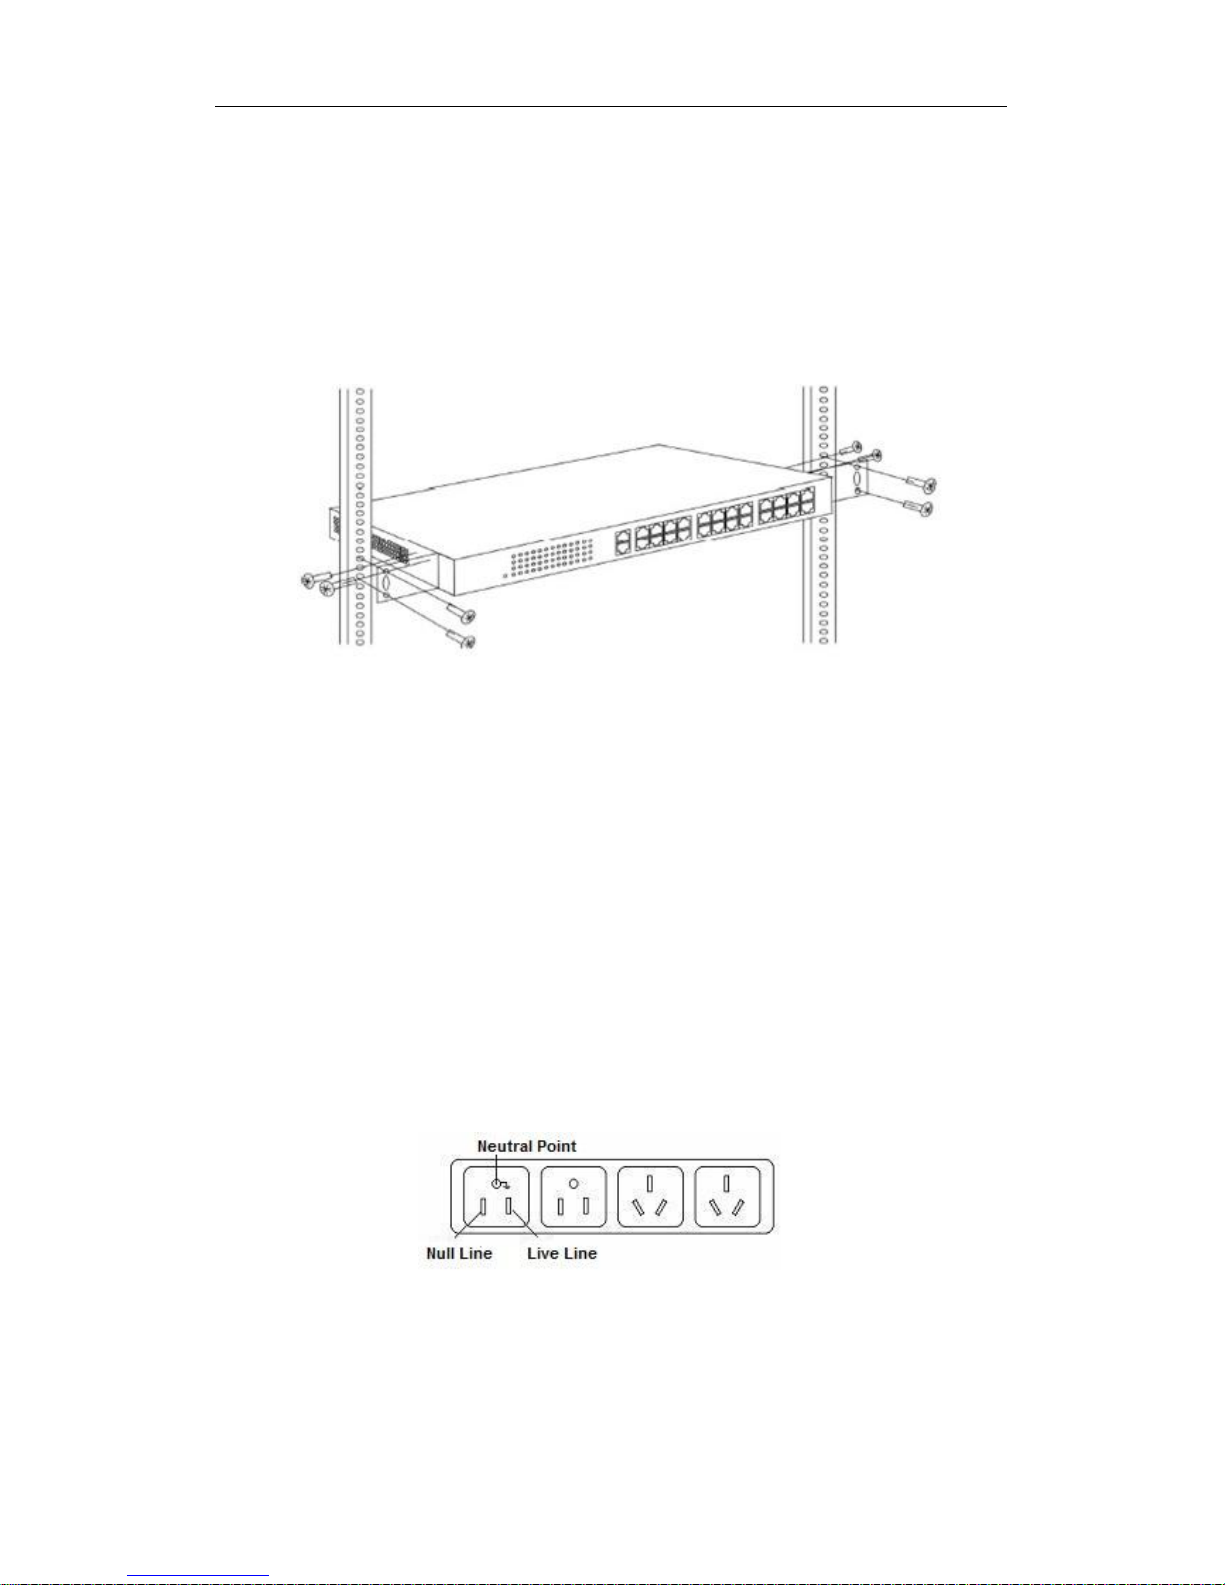
3.2.1 Select of AC Power Socket
The neutral one-phase 3-wire power socket is advised to adopt, or the
multifunctional PC power socket. The neutral point of power supply must be well
grounded, please check the grounded power supply before operation.
Picture 3.2.1 one-phase 3-wire power socket
3.2.2 Connection of AC power cord
Step one: please connect one end of power cord to the power jack on the switch
rear panel,Connect the other end to the AC power socket.
Page 9
User’s Guide
Page 9 of 54
Step two: check the power indicator(PWR) on the front panel, if the LED is on,
connection is
Successful.
3.3 Test after Installation
Make sure the working voltage is the same with the rated voltage of switch.
Check the connection of grounded cord.
Check the connection of configuration cable and power input cord.
If the interface cable is partly deployed outdoor, please check the connection of
anti-thunder
AC power strip and interface anti-thunder device.
Page 10
User’s Guide
Page 10 of 54
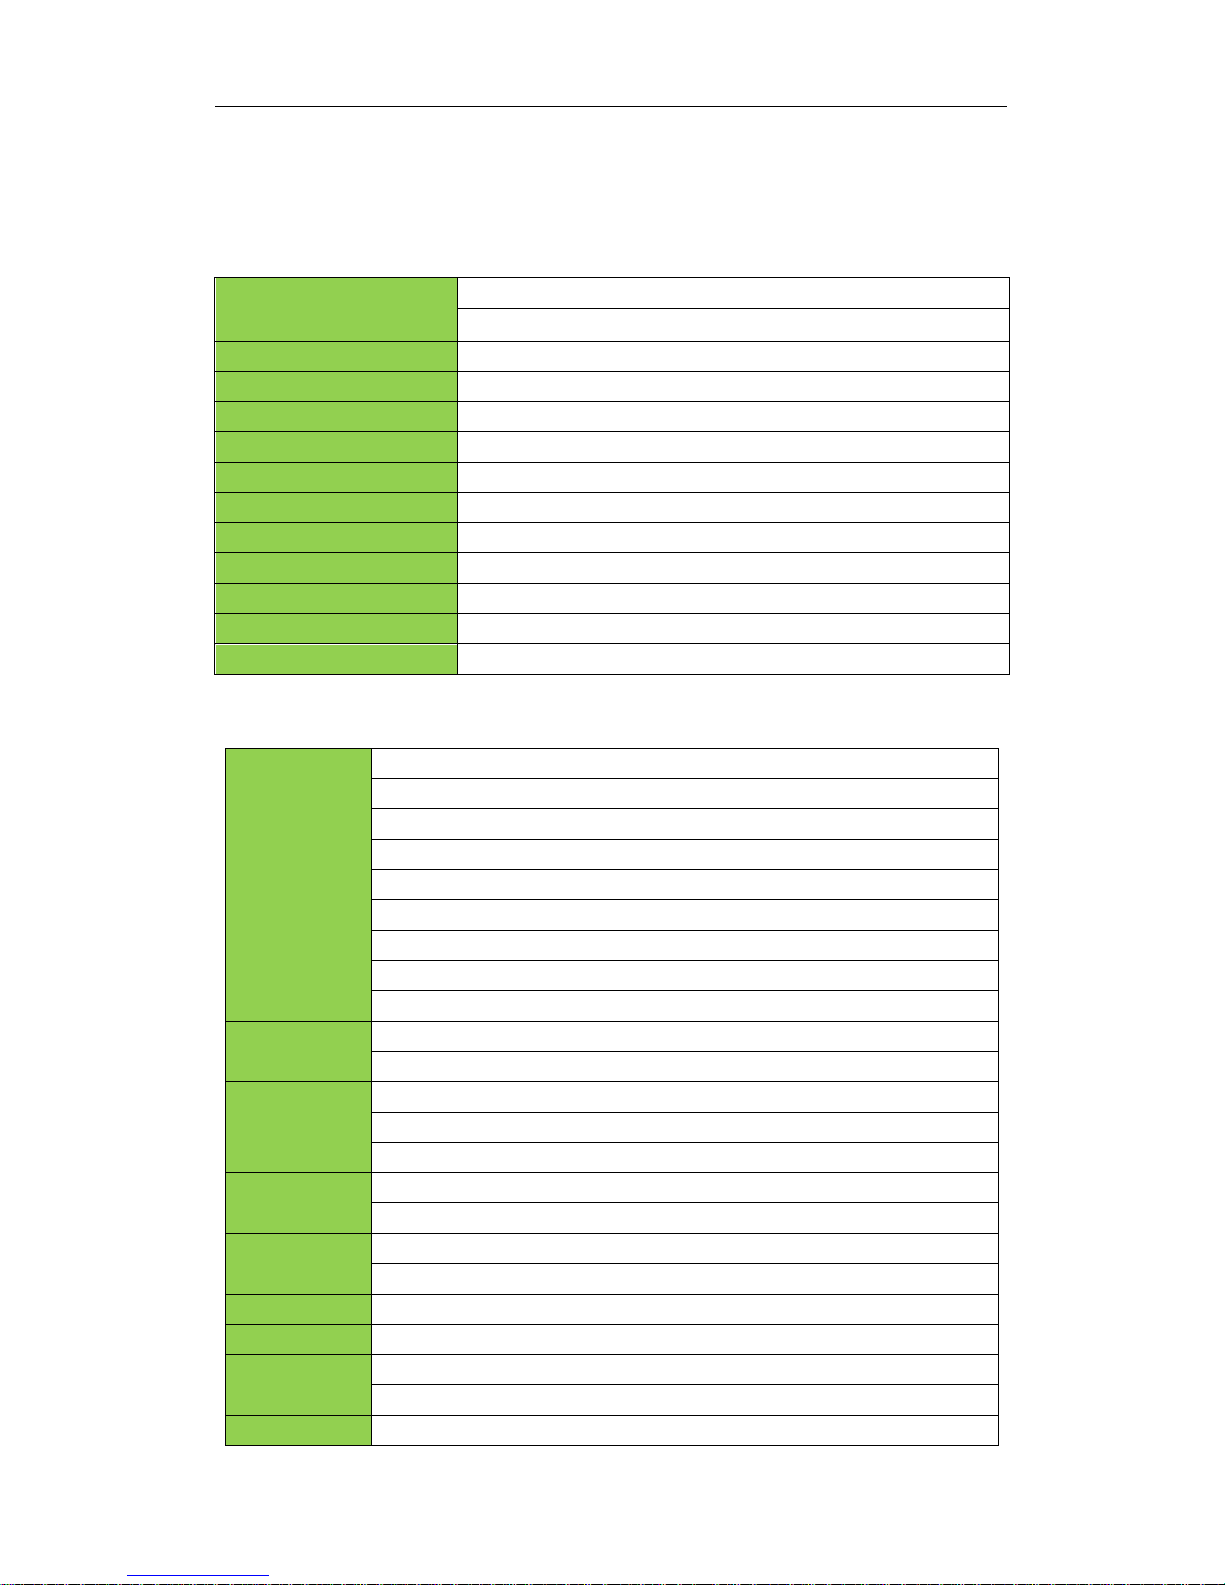
Chapter 4 Technical Specifications
4.1 Hardware Features:
Service Ports
16*1000 Base-X SFP
8*10/100/1000 Base-T
Management Port
1* Console port
Switching Capacity
≥48Gbps
Packet Forwarding Capacity
36Mpps
Operation Temperature
-20~50°C
Storage Temperature
-40~70°C
Operation Humidity
10%~90%(non-condensing)
Storage Humidity
5%~95%(non-condensing)
Dimensions
440(L)×285(W)×44.5(H) mm
Weight
<4Kg
Input Voltage(AC)
AC:110~240V/50~60Hz
Power Consumption
<30W
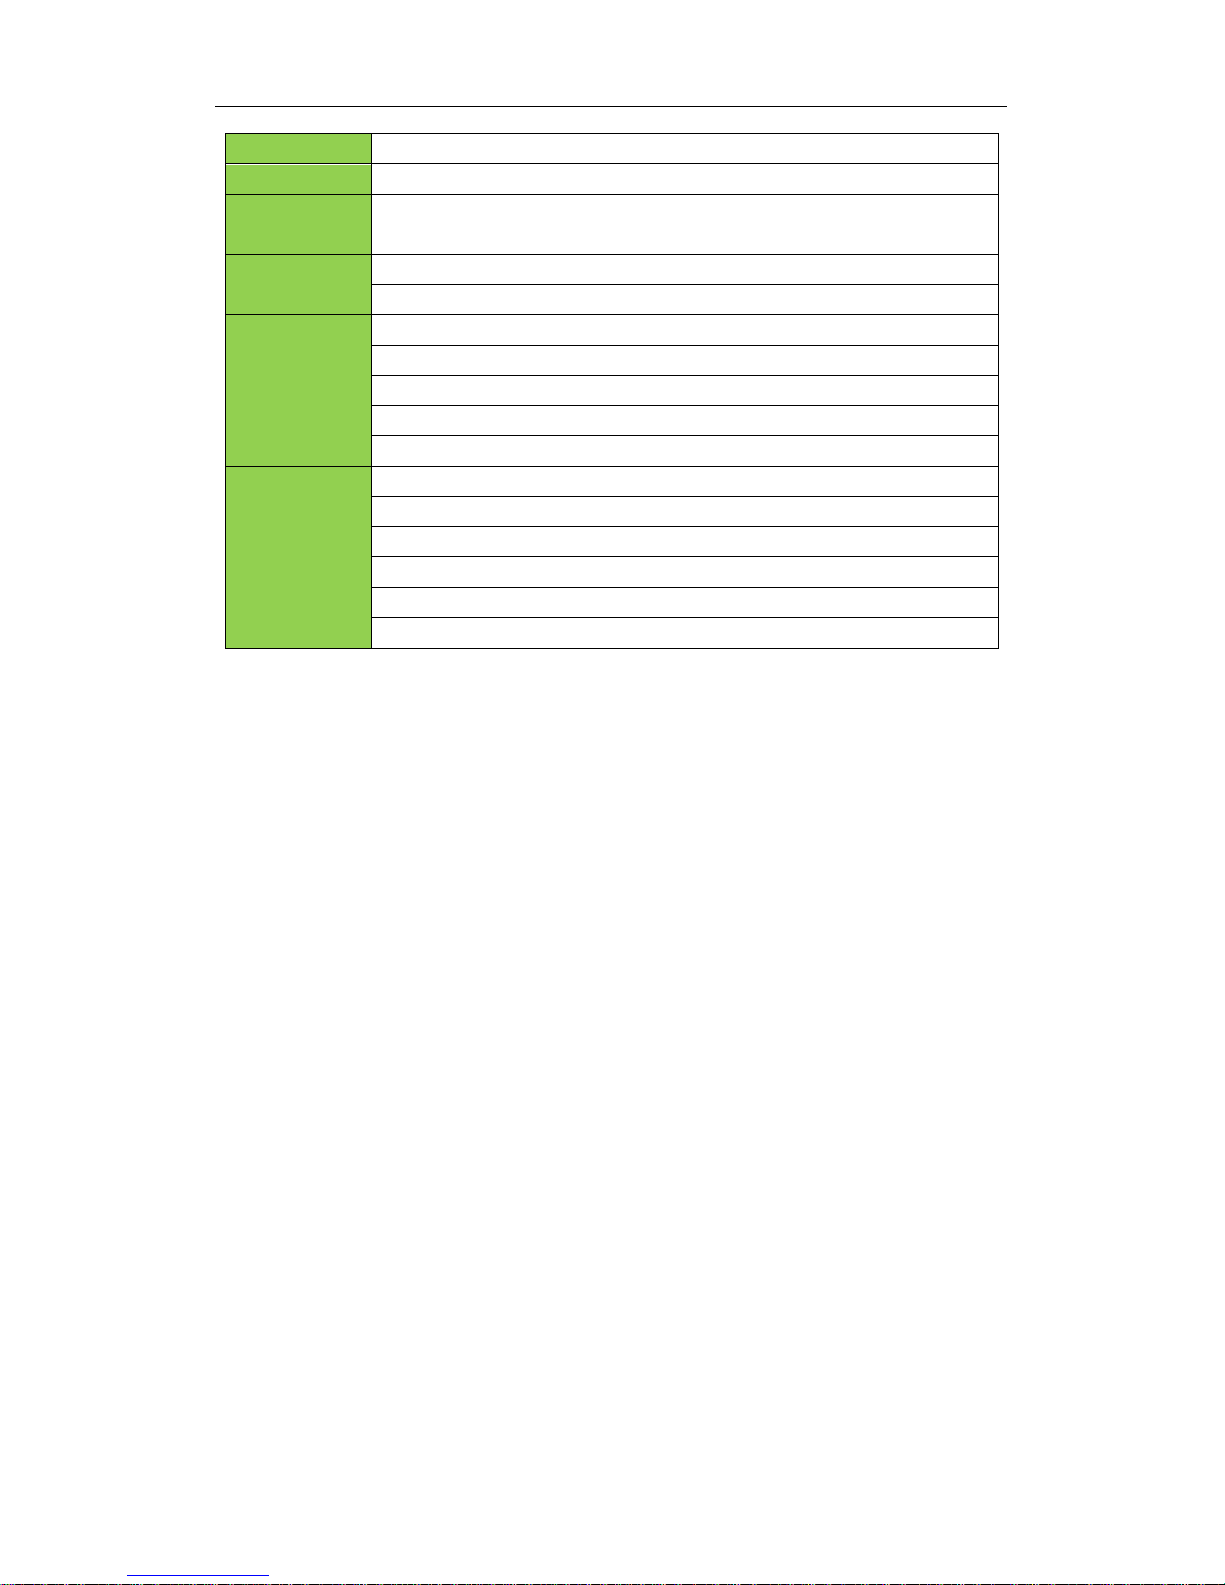
4.2 Software Features:
Protocol
and Standards
IEEE 802.3ad, Static or Dynamic Link Aggregation;
IEEE 802.3u,100 BASE-TX;
IEEE 802.3ab,1000 BASE-T;
IEEE 802.3z,1000 BASE-X;
IEEE 802.3x,Full-Duplex Flow Control;
IEEE 802.1q,VLAN;
IEEE 802.1p,QoS/CoS;
IEEE 802.1d, Spanning Tree Protocol;
IEEE 802.1w,Rapid Spanning Tree Protocol;
MAC Address
16K MAC addresses;
Support auto-update, two-way learning;
VLAN
256 VLANs;
Port-based VLANs;
VLANs based on IEEE 802.1q;
Spanning Tree
STP Spanning Tree Protocol;
RSTP Rapid Spanning Tree Protocol;
Port
Aggregation
12 aggregation groups,each containing up to 12 ports;
Static aggregation and dynamic aggregation;
Port Mirroring
Many-to-one mirroring(that is, multiple mirroring ports, and one monitor port)
Ring Guard
Ring detection and avoidance
Traffic Control
Back-pressure traffic control under Half-Duplex mode
IEEE 802.3x traffic control under Full-Duplex mode
Flow Rate
Port-based ingress or egress rate limiting
Page 11
User’s Guide
Page 11 of 54
Limitation
Multicast
IGMP Snooping
Storm
Suppression
Support the suppression of broadcast, multicast, DLF flooding and ICMP flooding
Security
Binding of the User port, IP addresses and MAC addresses;
802x1 port authentication;
QOS
SP(Strict Priority);
WFQ (Weighted Fair Queuing);
WRR (Weighted Round Robin);
802.1p (Port Queuing Priority);
DSCP Priority(Differentiated Service Code Point) ;
Configuration
and
Management
Uploading or downloading of the configuration data;
Uploading of upgrade patch;
WEB-based reset to factory defaults;
WEB-based interface management;
CLI interface management;
SNMP management;
Page 12
User’s Guide
Page 12 of 54
Part Two WEB Configuration Guide
Chapter 1 User Login
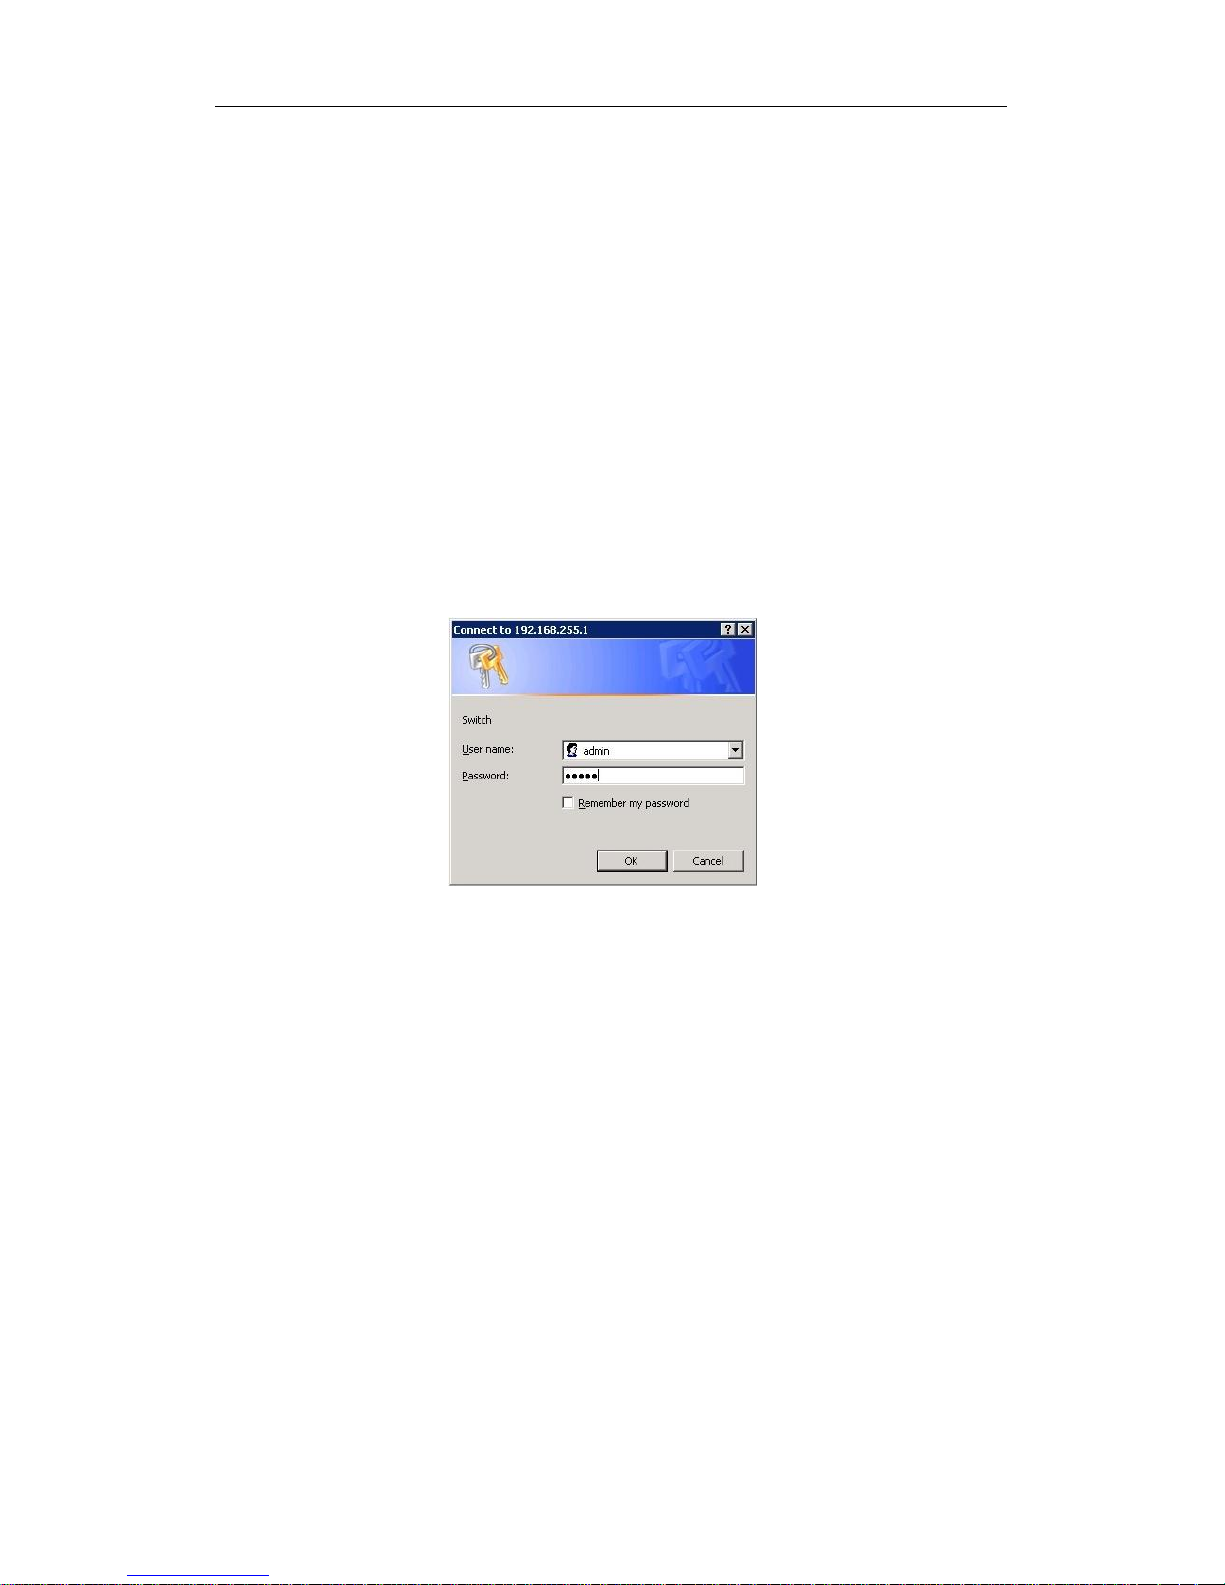
switch adopt Web-based interface management, the default IP is 192.168.255.1. Please
check the IP address of PC, the PC IP address should in the same network segment with
switch IP address, or the PC can’t access to manage the switch. After the setting of IP
address, please input 192.168.255.1 in the browser to access the configuration interface of
switch.
The Web management interface consists of four modules, which are device information,
basic configuration, advanced configuration and system maintenance.
Picture 1.1.1 Login Page
Enter user password in the above login page, the default password is admin. The system only
support single user login, other logins will be refused until the user logs out.
If there isuser IP conflict, it suggests the last user didn’t log out successfully. Please
reboot the device or try to log in again180s later.
The user is advised to reset the IP address and password after first time login, and make
sure the switch is not configured in the same network segment with DHCP server or
Internet Gateway device.
Page 13
User’s Guide
Page 13 of 54
Chapter 2 Device Status
2.1 System Status
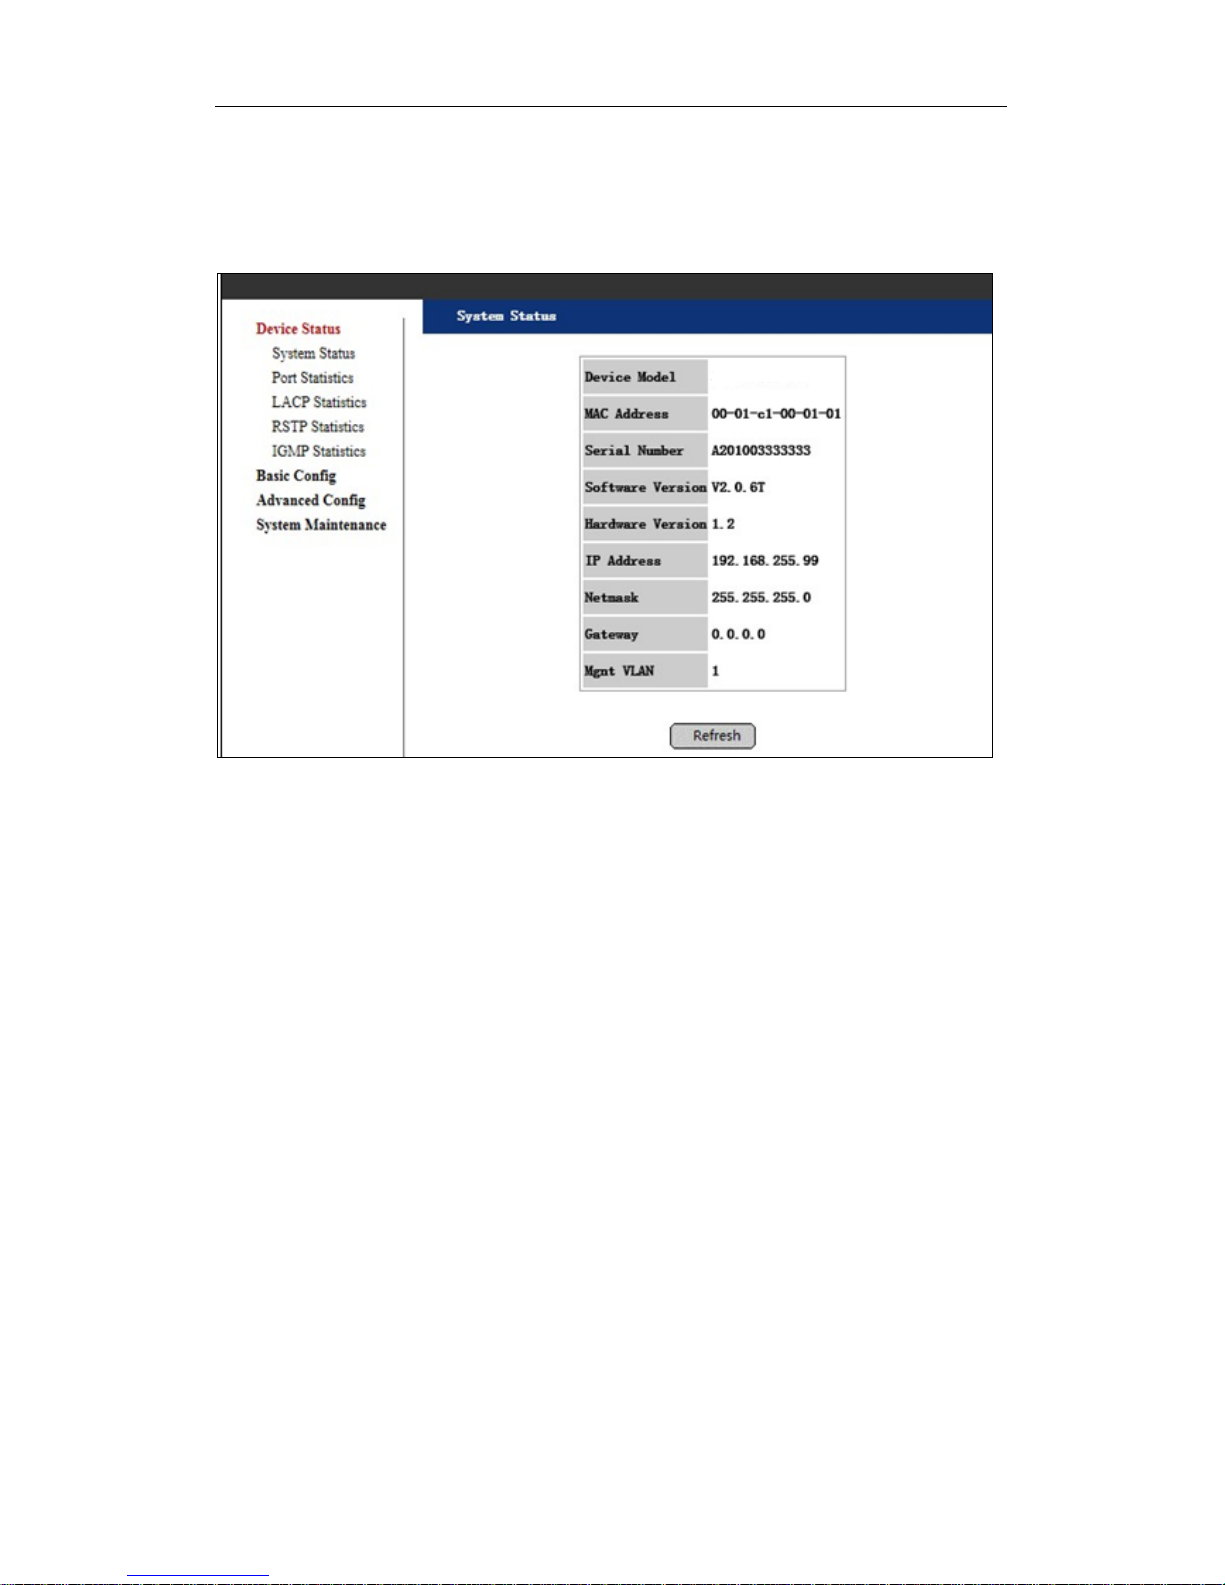
Picture 2.1.1 System Status
Device status can be checked in the above page, which contains: Device Model, MAC
Address,Serial Number, Software Version,Hardware Version, IP Address, Netmask,Gatway
and Mgnt VLAN.
Page 14
User’s Guide
Page 14 of 54
2.2 Port Statistics
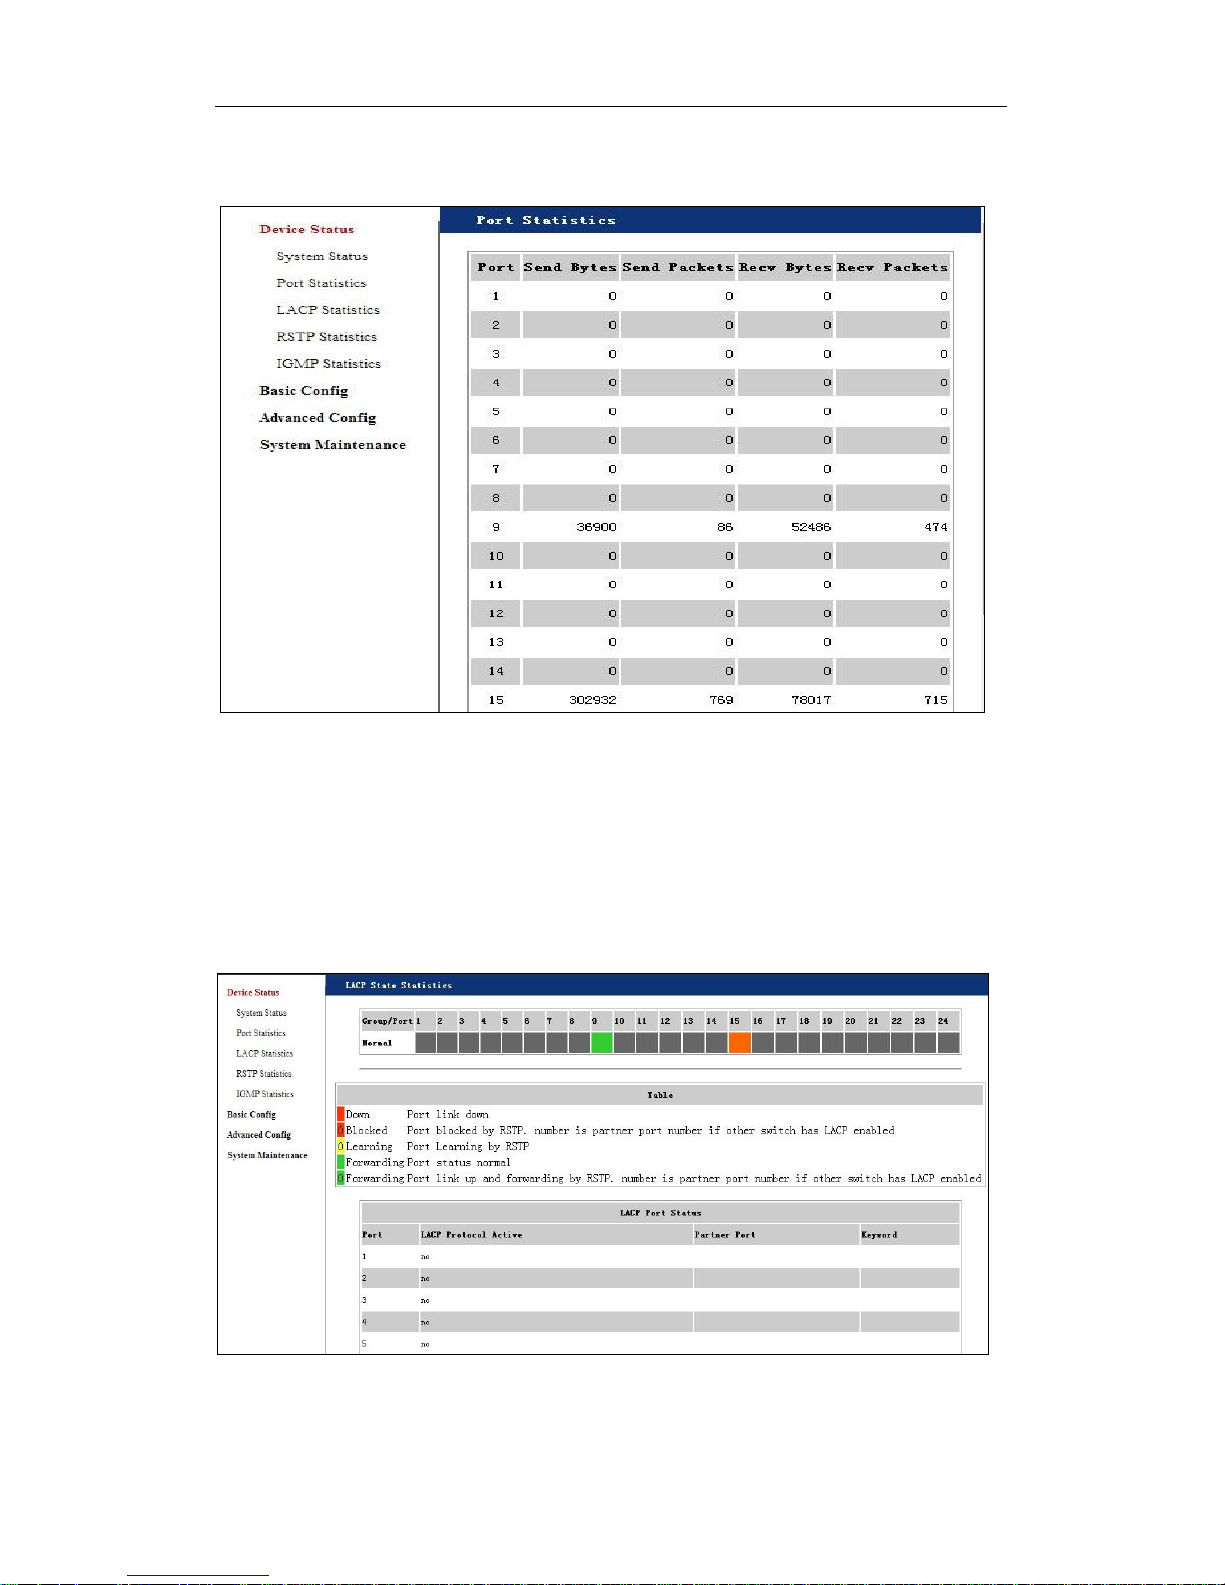
Picture 2.2.1 Port Statistics
This page allows user to check the send bytes,send packets, recv bytes, recv packets. If
there are too many wrong packets, it suggests the port has very poor working performance,
the user need to examine the connection of network cable or the partner network card.
The current software version doesn’t support real-time statistics refresh, please click
“Refresh” button to get new statistics.
2.3 LACP Statistics
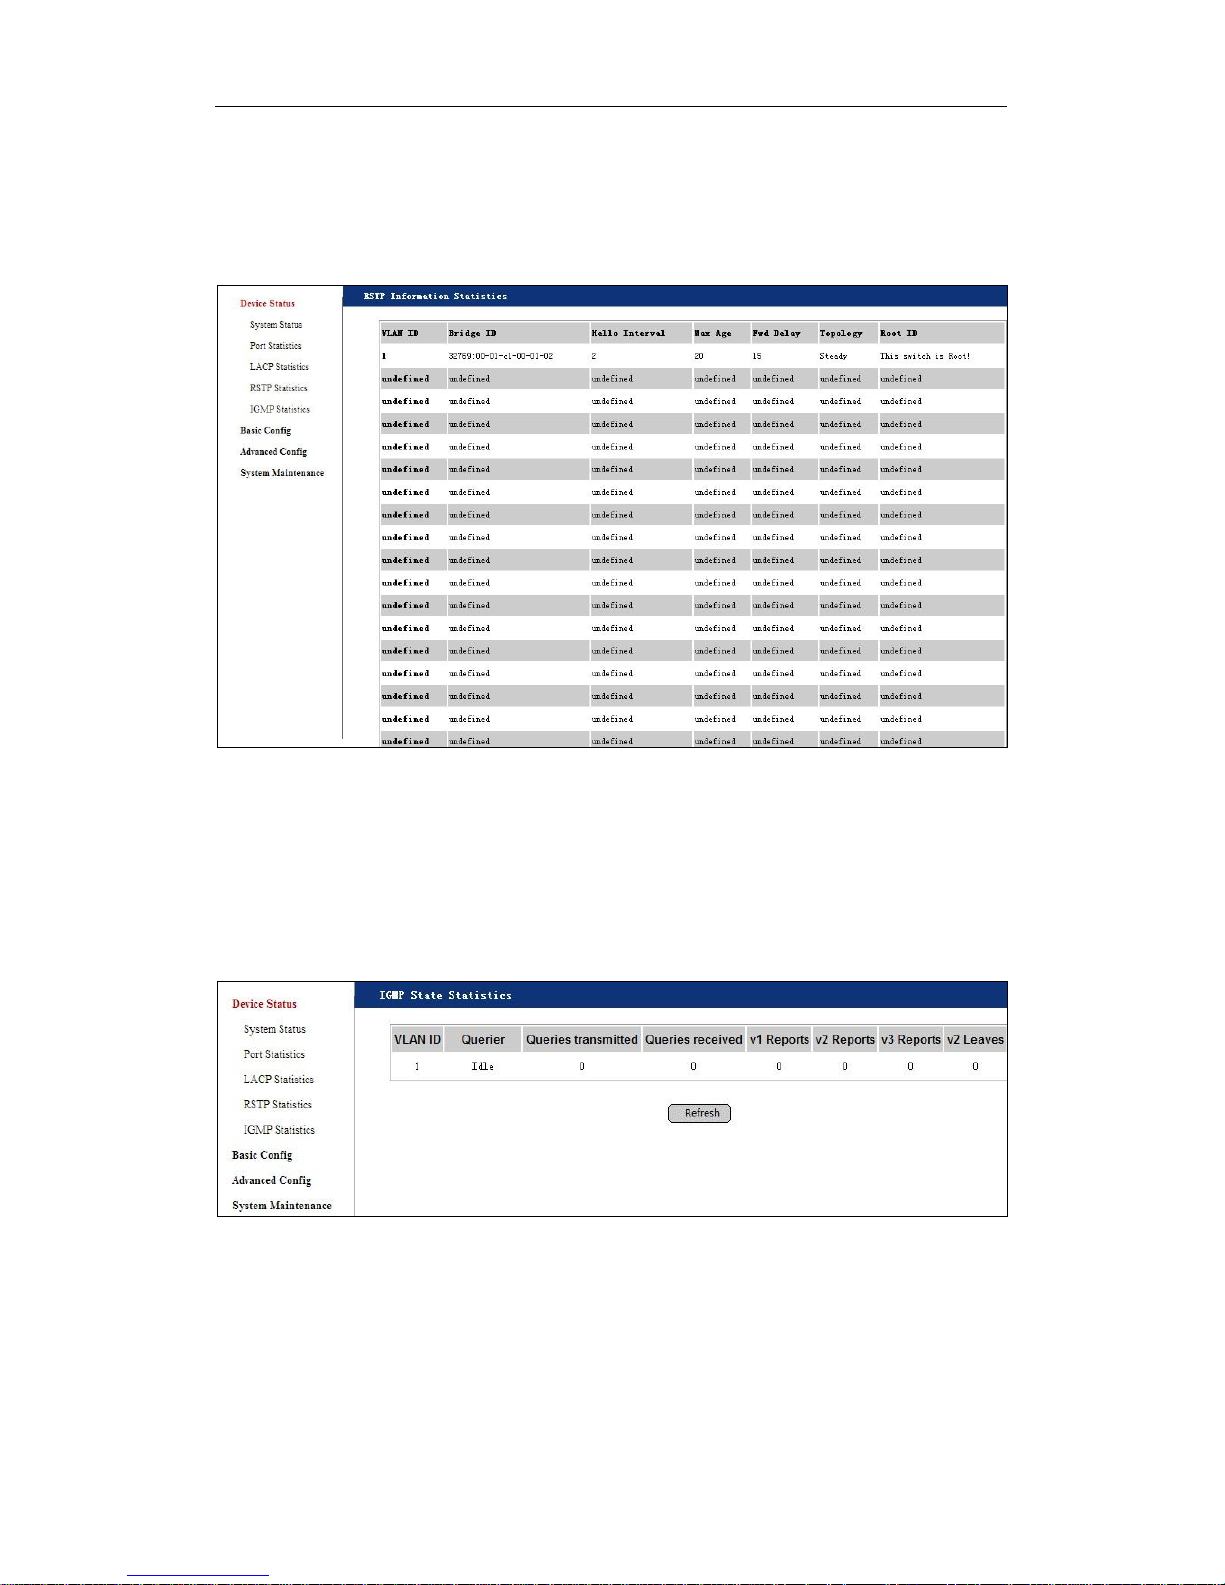
Picture 2.3.1 LACP Statistics
Users can check the LACP protocol running state of sing port in this page, the port state
Page 15
User’s Guide
Page 15 of 54
can be easily defined by marked colours(showed in above picture). Detailed LACP protocol
information is showed in this page, including partner port and keywords.
2.4 RSTP Statistics
Picture 2.4.1 RSTP Information Statistics
Users can find the RSTP bridge ID for every VLAN, and the basic RSTP information in
this page. In RSTP port status, the user can check VLAN ID, Path Cost,Edge Port,P2P Port,
Protocol and Port State.
2.5 IGMP Statistics
Picture 2.5.1 IGMP Statistics
Users can check the IGMP state statistics for current VLAN in this page.
Chapter 3 Basic Config
Page 16
User’s Guide
Page 16 of 54
3.1 System Config
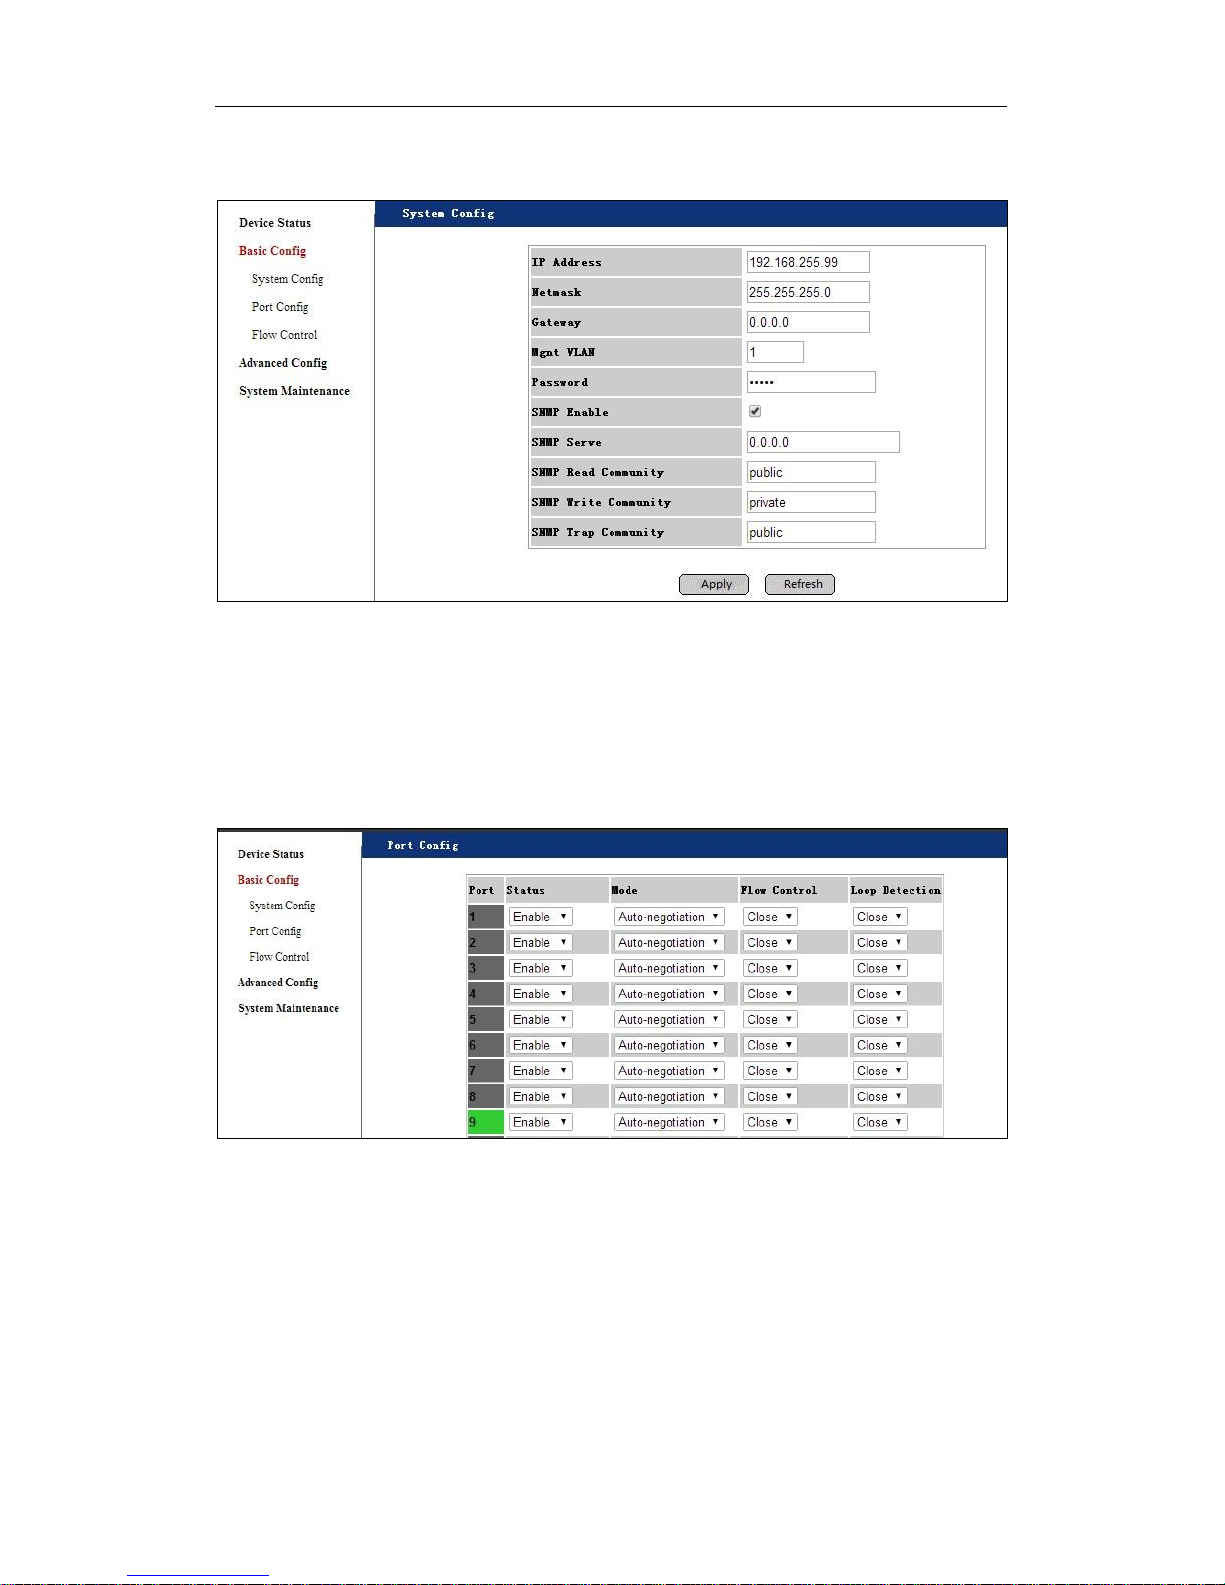
Picture 3.1.1 System Config
The user can check or modify IP address, netmask,gateway,mgnt VLAN, password and
SNMP configurations in this page.Click “Apply” to confirm the modification. Notice: Don’t
modify the netmask randomly, failed login may be caused by improper modification.
3.2 Port Config
Picture 3.2.1 Port Config
Port Status: The user can enable or disable a port in this page.Click “Enable” to open the port,
click “Disable” to close the port, the default setting is “Enable”.
Port Mode: 6 modes can be configured:Auto-negotiation,10 Half,10 Full,100 Half, 100 Full
and1000 Full. Default mode is Auto-negotiation, can be changed in pull-down list.
Flow Control: This function is defaulted closed, open it when needed.
Loop Detection:The function is defaulted closed, open it when needed.A port will be blocked
to cut the loop when loop is detected.( Notice: the port link indicator in front panel will be still
Page 17
User’s Guide
Page 17 of 54
on when the port is blocked, for the physic connection is existed; while the link indicator on
the top of web management pages will be off.)
3.3 Flow Control
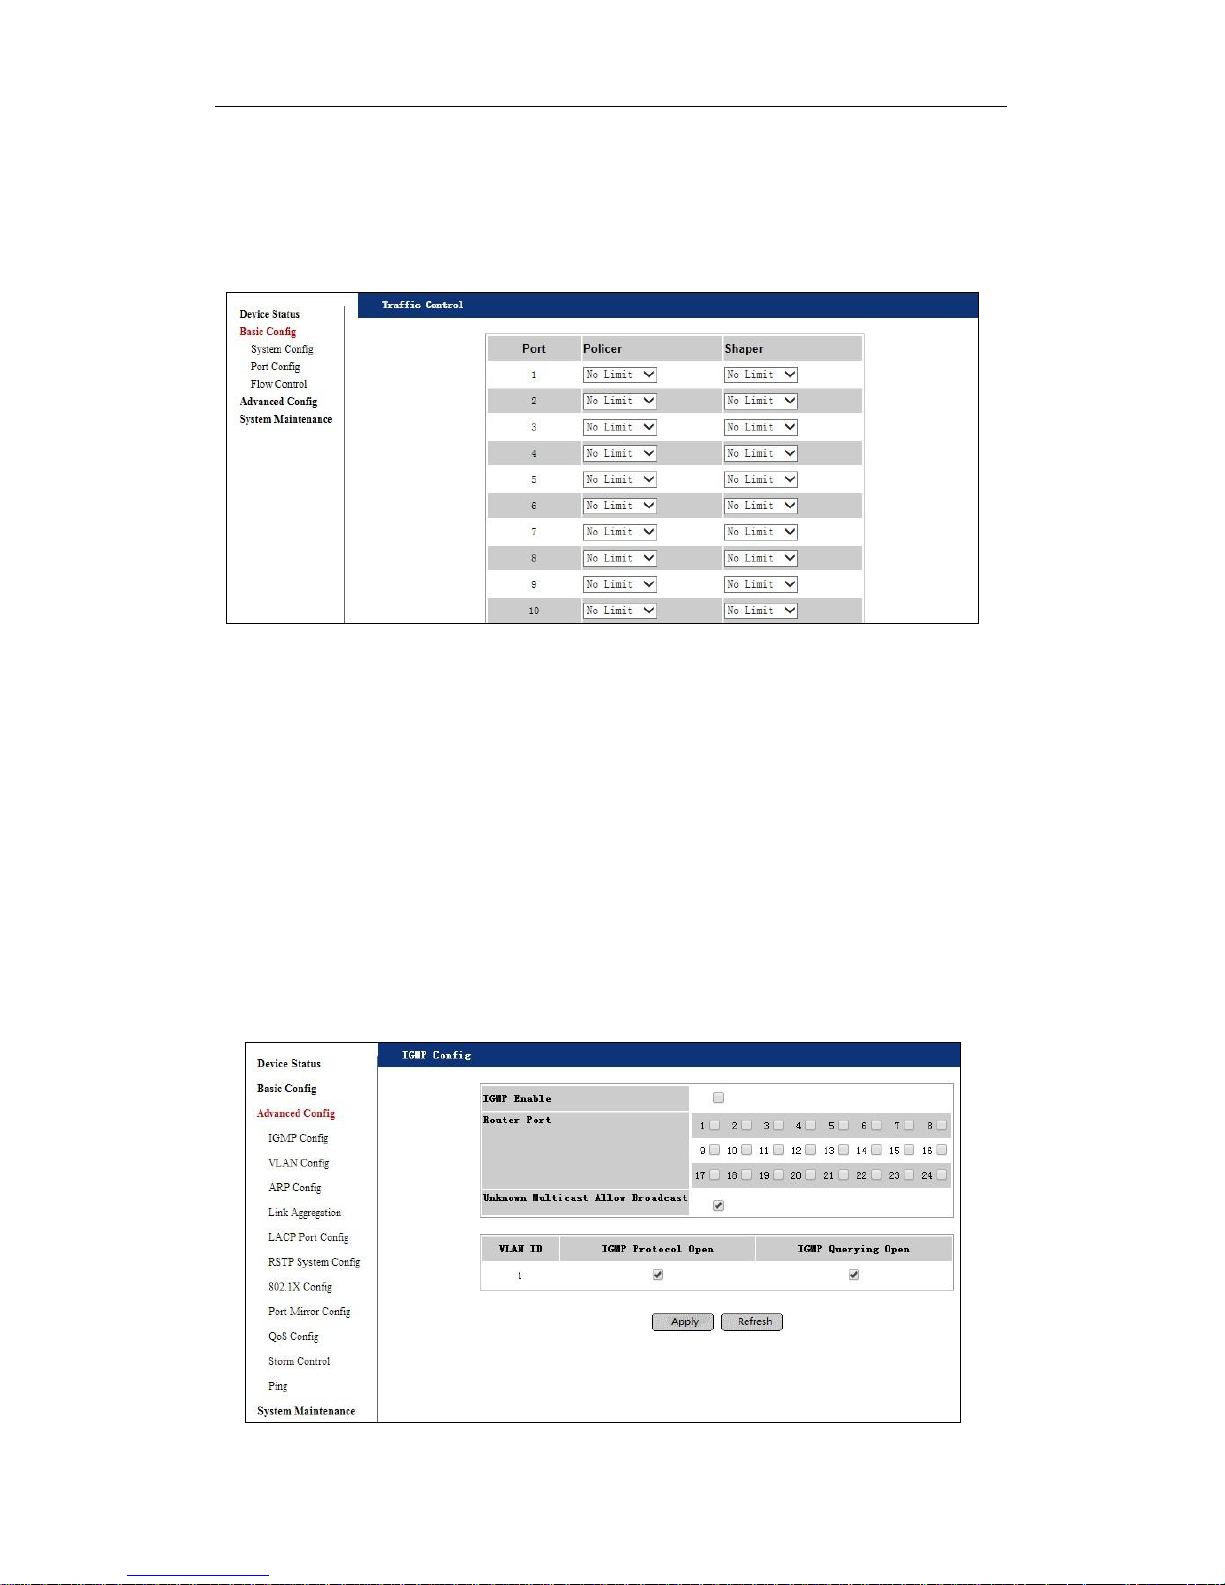
Picture 3.3.1 Flow Control
Users can define the bandwidth settings for specified egress and ingress interfaces in this
page. Flow control allows the user to limit maximum burst ingress flow, the port flow control
function works when the bandwidth limit is exceeded. There is no default bandwidth limit,
users can set the limit accordingly, limit shoud be in the range of 128kbps-3968kbps. Flow
shaping refers to the limit of maximum egress flow. The flow shaping function works when the
limit is exceeded. The limit is not defaulted, please set the limit accordingly, the limit should
be in the range of 128kbps-3968kbps.
Chapter 4 Advanced Config
4.1 IGMP Config
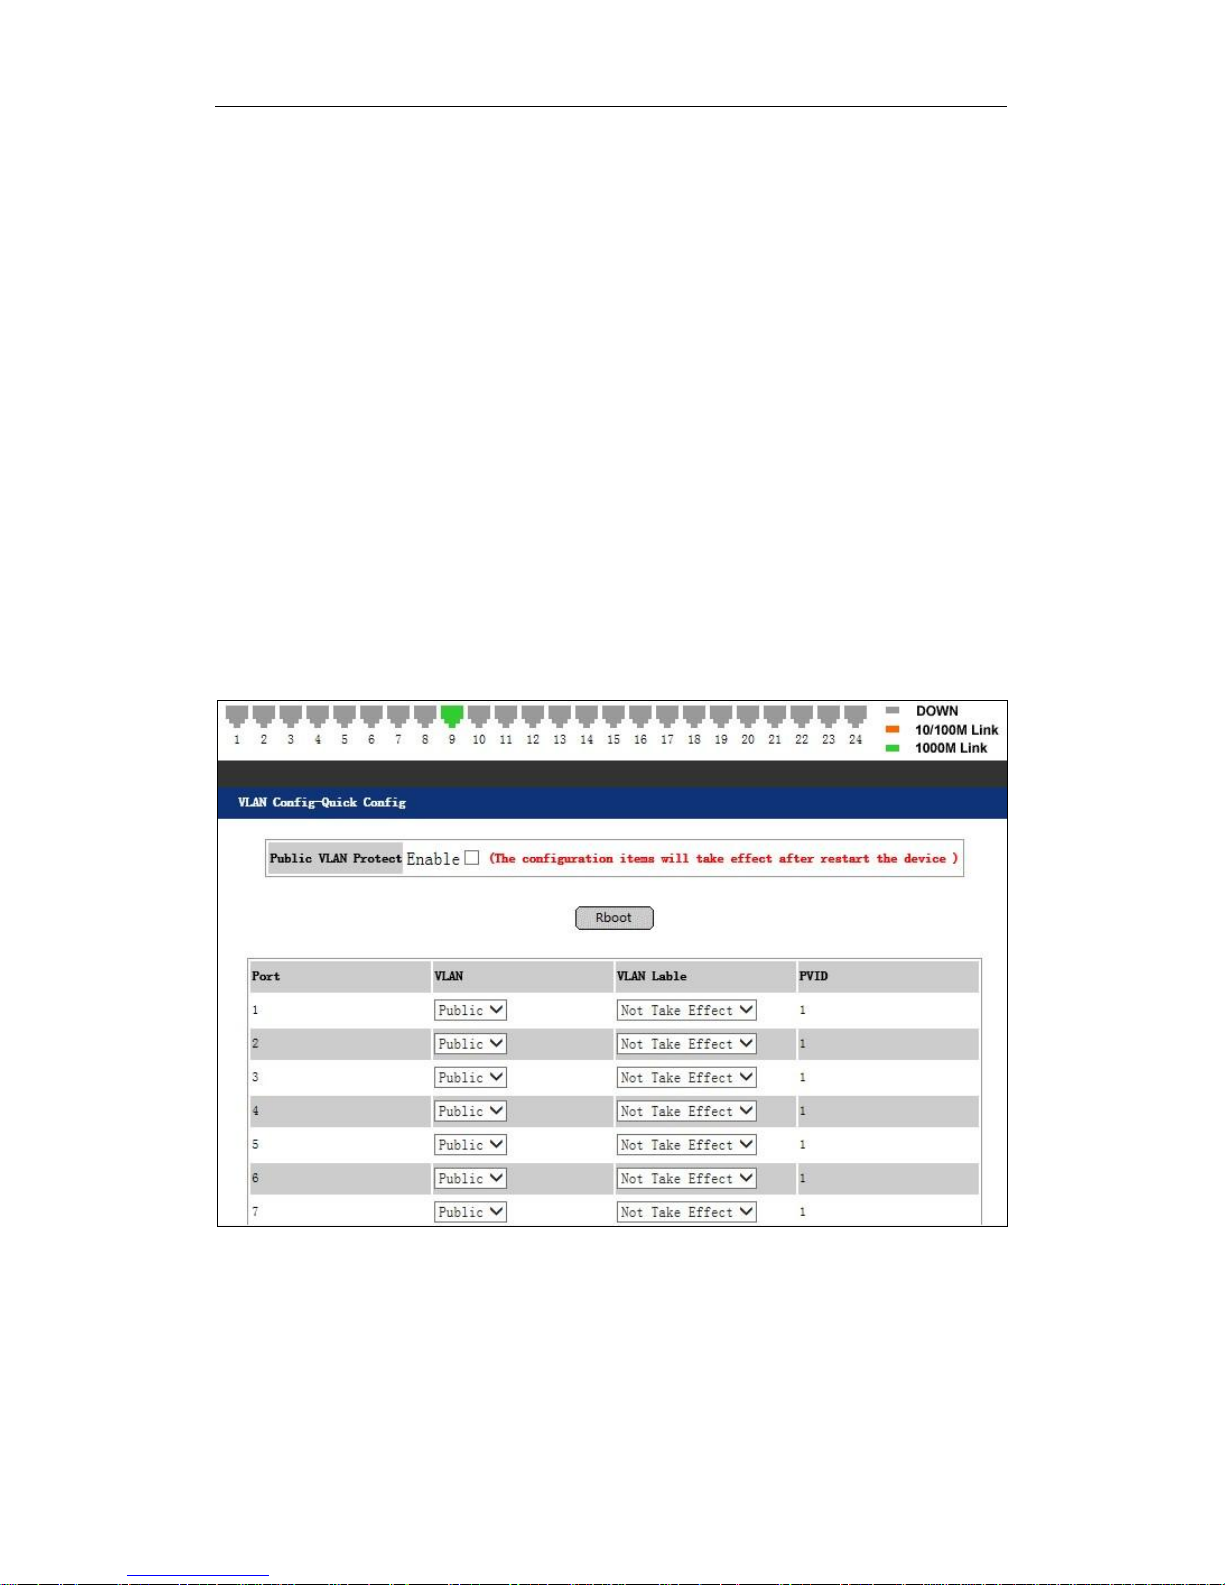
Picture 4.1.1 IGMP Config
Page 18
User’s Guide
Page 18 of 54
Showed in above is the IGMP multicast configuration page, the router port is static router port,
not aging. If a port is not configured as static router port, the switch define the port has a
connection with IGMP router(directly or indirectly)when it receives IGMP query messages
and the port will be recorded as dynamic router port .
The device snoops the IGMP messages by IGMP snooping, and build mapping relationship
between the device ports and multicast addresses.
The IGMP querying function refers to the IGMP router regularly send query messages to IP
multicast members, and the IP multicast members send back report messages to confirm the
multicast routing is effective. The query messages are divided into specified queries and
general queries. If the router is not working and can’t send out query messages, users can
configure the switch as an alternative of the router and send our query messages. Thus, the
IP forwarding path downstream the switch won’t get influenced and aged.
4.2 VLAN
The system provides two types of VLAN configuration: one is Quick Config for naive users to
do some simple VLAN distribution. The other is Advance Config for senior users who have
complex requirements on VLAN.
4.2.1 Quick Config
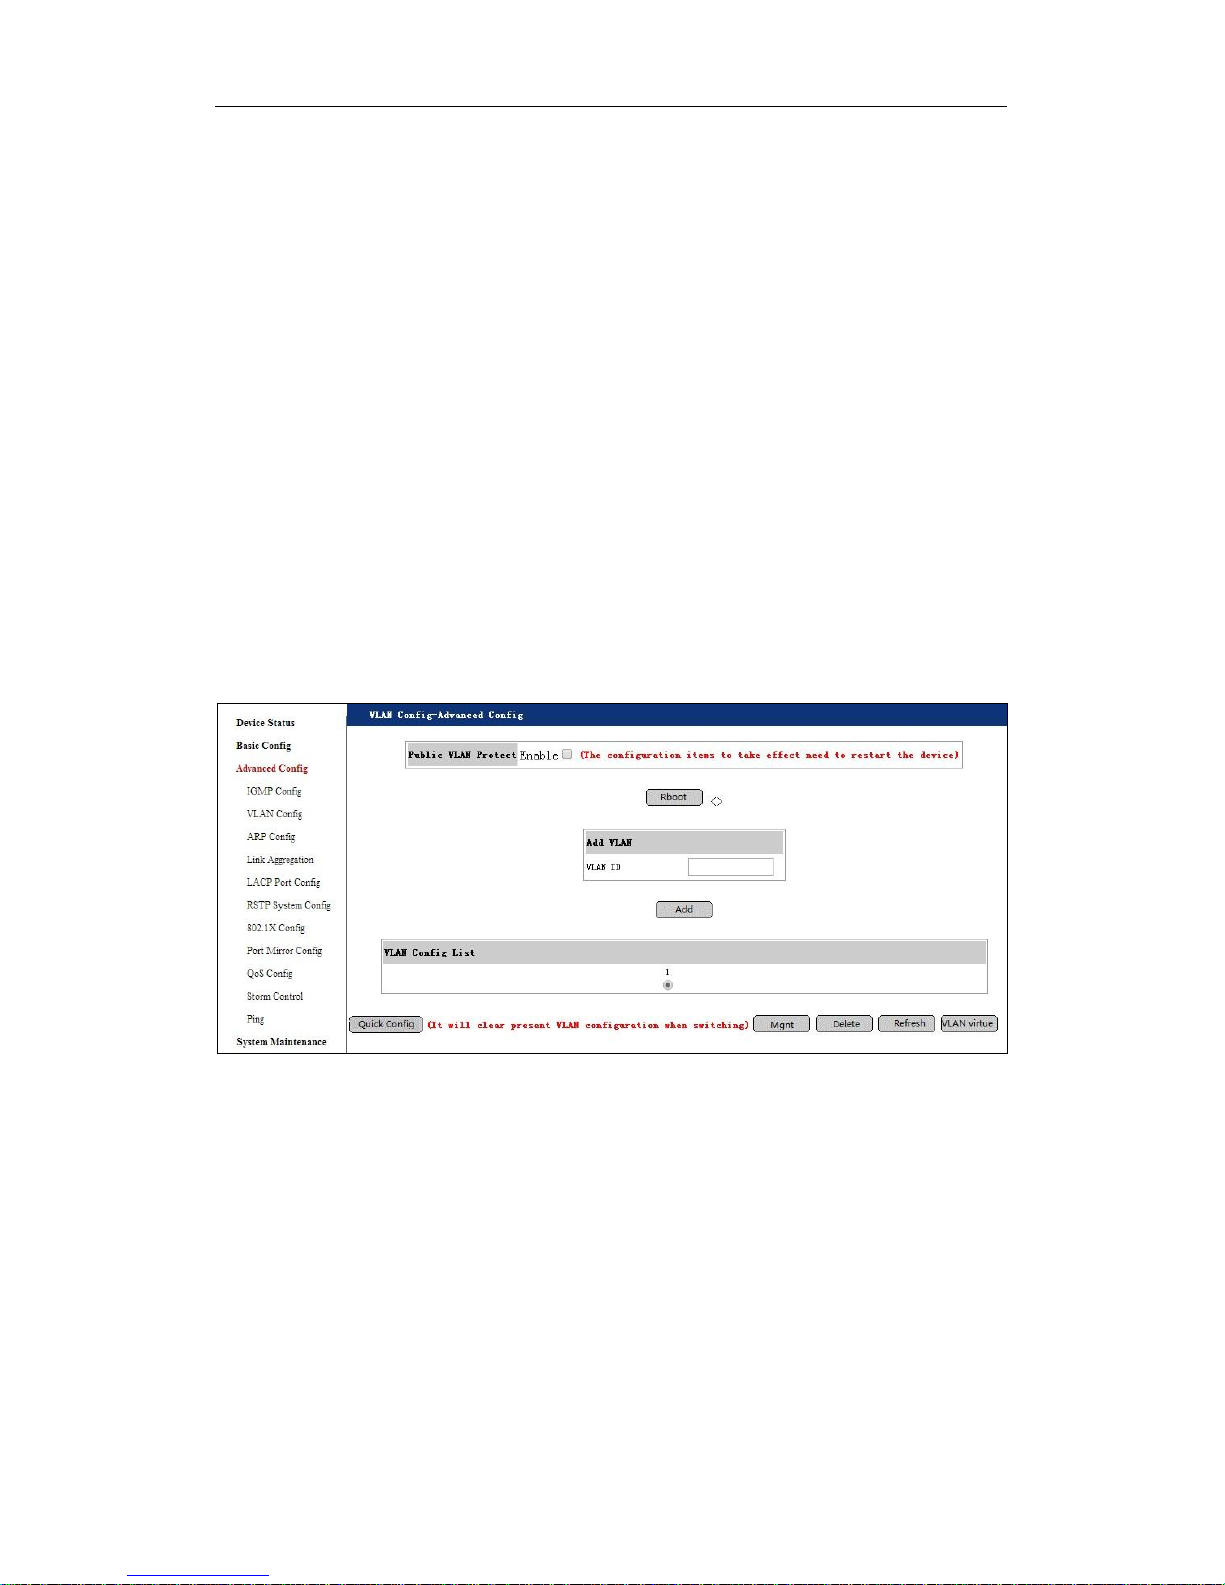
Picture 4.2.1 Vlan Rapid Configuration
“Public VLAN Protect” is an isolating function of VLAN. When the switch has public
ports( also named as public VLAN), users can effectively get VLAN data isolated by select
“Public” .Thus,the low-speed sources among the public ports won’t influence the visit speed
of other ports. And if only the normal VLAN function needed, please do not enable this
function(the default state is diable).The enable of public VLAN protect function will take effect
after rebooting device, please click reboot button to hot reboot the device and log in one
Page 19
User’s Guide
Page 19 of 54
minute later.
VLAN Quick Config supports VLAN IDs range from 1 to 24, maximum supports 24 VLANs.
There are 24 ports showed in the top of page, and each port has a pull-down list to select
from No.2~24 VLAN or the “Public” VLAN. Users can add specified ports into different VLAN
and configure one or more ports as public VLAN.Usually the following ports will be configured
as public VLAN: general uplink port, server port, router port , printer port and other ports).
Click”Binding” button to confirm the configuration. After this configuration, PVID configuration
is not needed, the system will automatically configure PVID according to the VLAN IDs. In
normal configuration of public VLAN, the VLAN Label is “Not Take Effect”by default, no select
needed. ( Notice: When configure the VLAN, the switch port connects with this
administrative PC should be in the managment VLAN which is public VLAN in default
setting.)
Click “ delect” botton to clear all the configuration.
If more VLAN configuration functions are needed, please click “ Advanced config” button in
the bottom of this page. The quick config information will be cleared when entering into
advance config page.
4.2.2 Advance Config
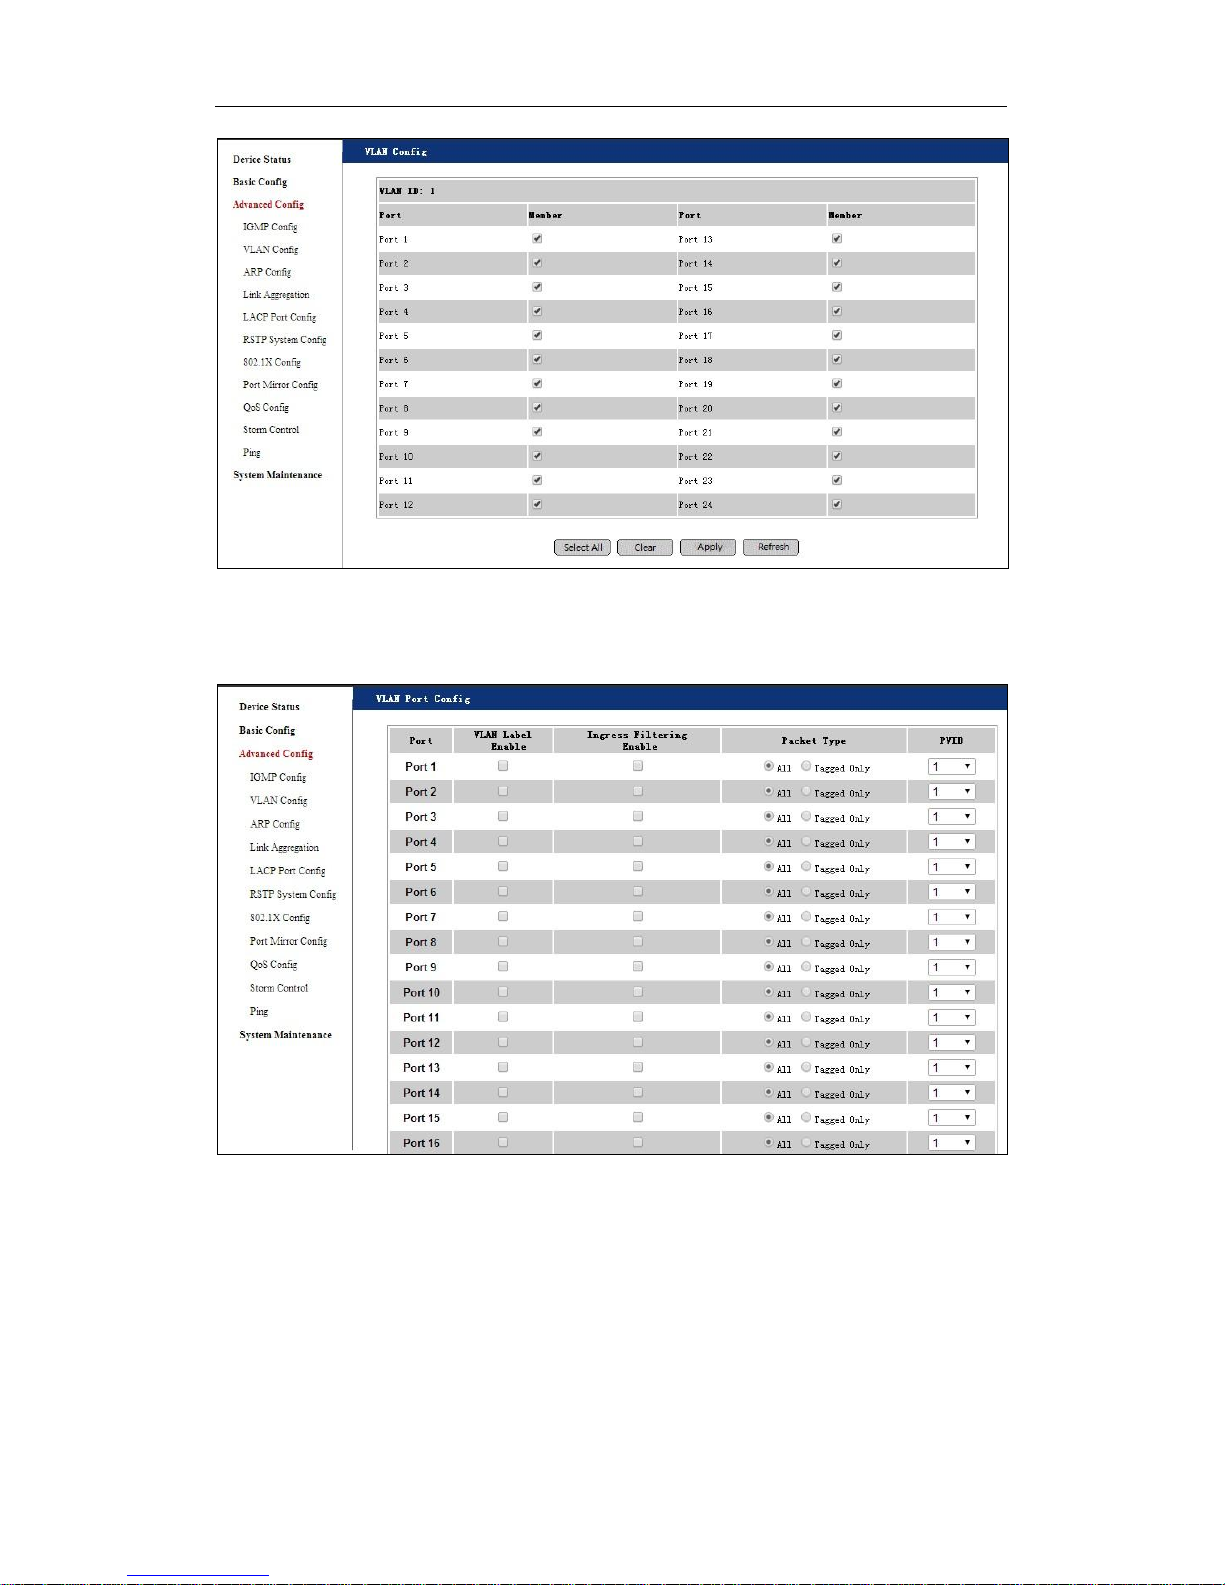
Picture 4.2.2 VLAN Advance Config
The user can create or delete VLAN in advance config. Currently support a VLAN ID
range of 1~4094, support maximum 255 VLANs.
Click”Mgnt(management)” botton to enter into below page and VLAN members can be
added or deleted in this page.
Page 20
User’s Guide
Page 20 of 54
Picture 4.2.3 VLAN Member Management
Click “ VLAN Virtue” botton to configure basic VLAN features.
Picture 4.2.4 VLAN Property Configuration
Beside VLAN distribution, users can also configure VLAN features. “VLAN Label Enable”
means port transmits tagged packets.”Ingress Filtering Enable” means when receiving a
mismatched VLAN packet,refusing to learn the address. “Packet Type” refers to what types of
packets can be received, tagged only or all. PVID means the default VLAN to get untag
packets, when a port is distributed to a specified VLAN, PVID need to be configured.
Case One. Public VLAN Mode
Page 21
User’s Guide
Page 21 of 54
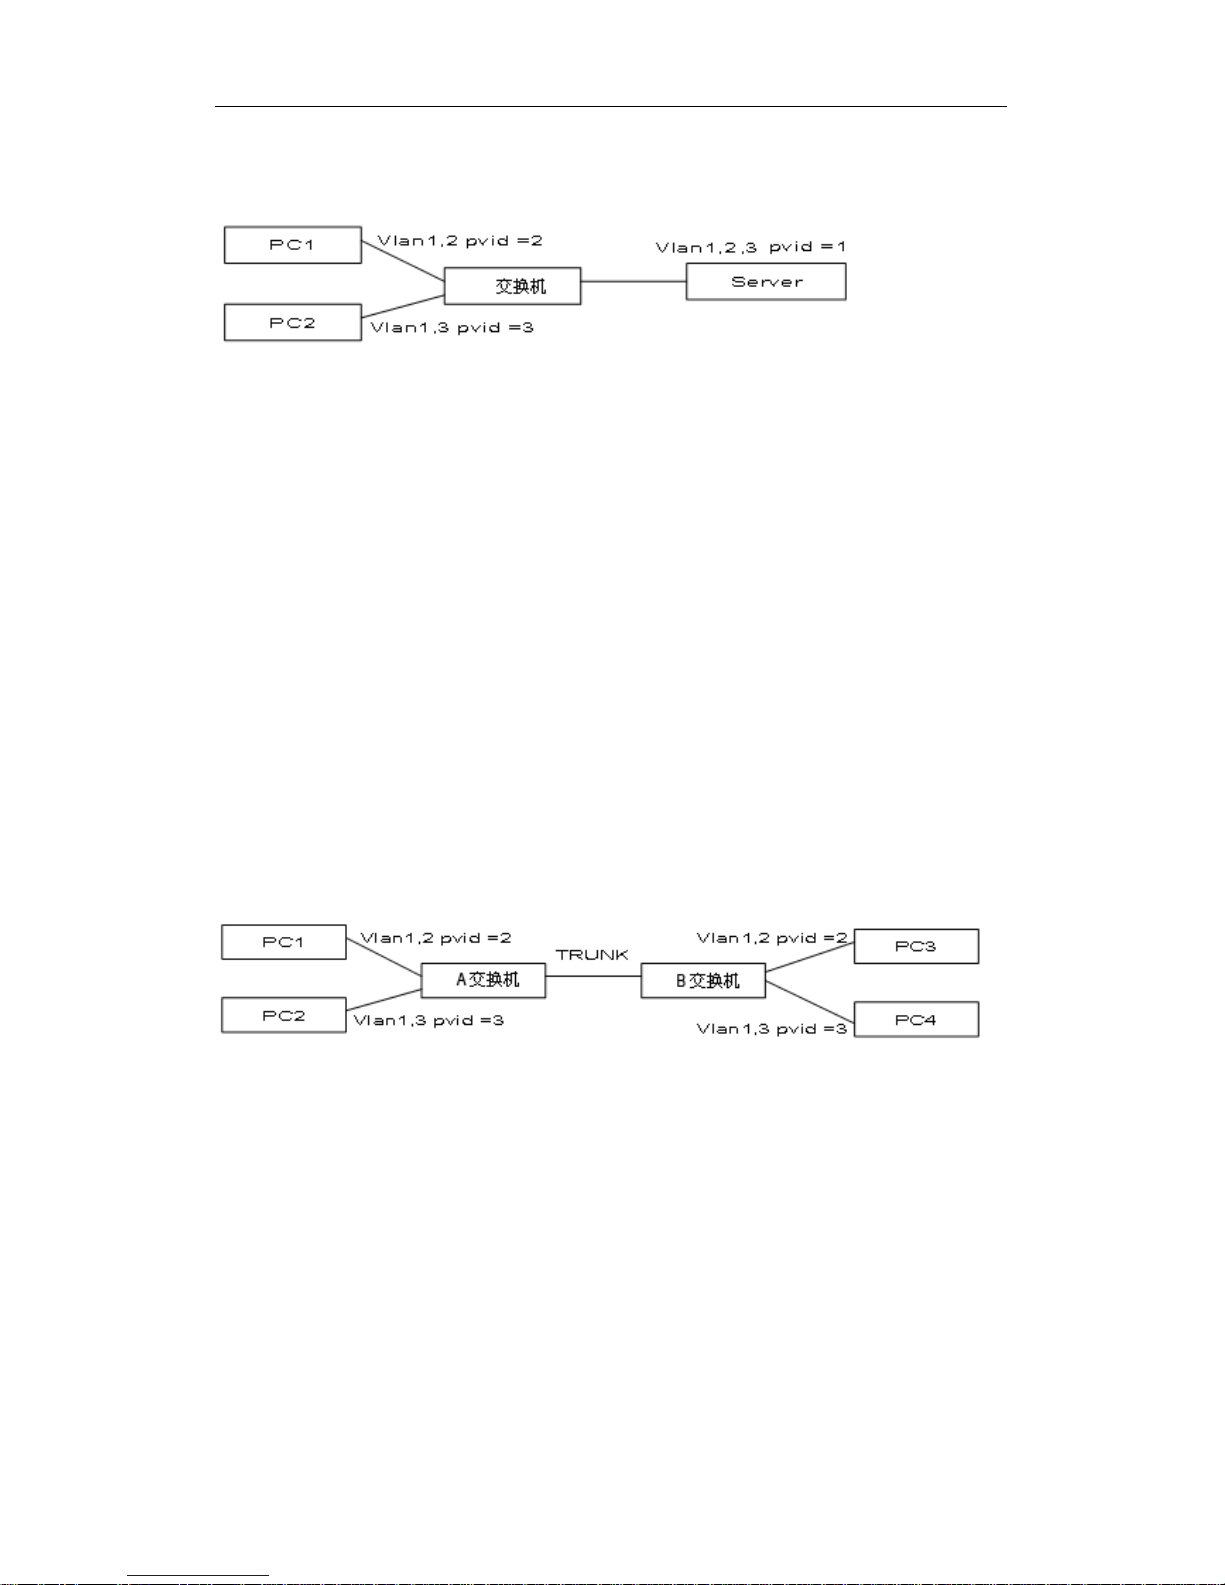
Two PCs: PC1 and PC2, connecting both PCs to Internet, but cannot access to each other.
The networking as follows:
Operation Steps:
Step One: Enable public VLAN protection function and log in after rebooting the device.
Step Two:Create a VLAN2, enter into VLAN member management page, configure PC1
port(named as Port 1) and Server port(named as Port 24) into VLAN2 and press
“ Application” to confirm.
Step Three:Create VLAN3, enter into VLAN member management page, configure PC2
port(named as Port 2) and Server port(named as Port 24) into VLAN3 and press
“ Application” to confirm.
Step Four: Open VLAN property page, configure the PVID of Port 1(PC1 port) as 2,
configure the PVID of Port 2(PC2 port) as 3, configure the PVID of Port 24(server port) as 1.
Step Five: Test result is PC1 and PC2 can’t access to each other(distributed to different
VLAN, isolated), both PC1 and PC2 can access to the server(public VLAN port).
Case Two. Tag VLAN Mode
Four PCs:PC1,PC2,PC3,PC4. Networking requirement: PC1 and PC3 can access each
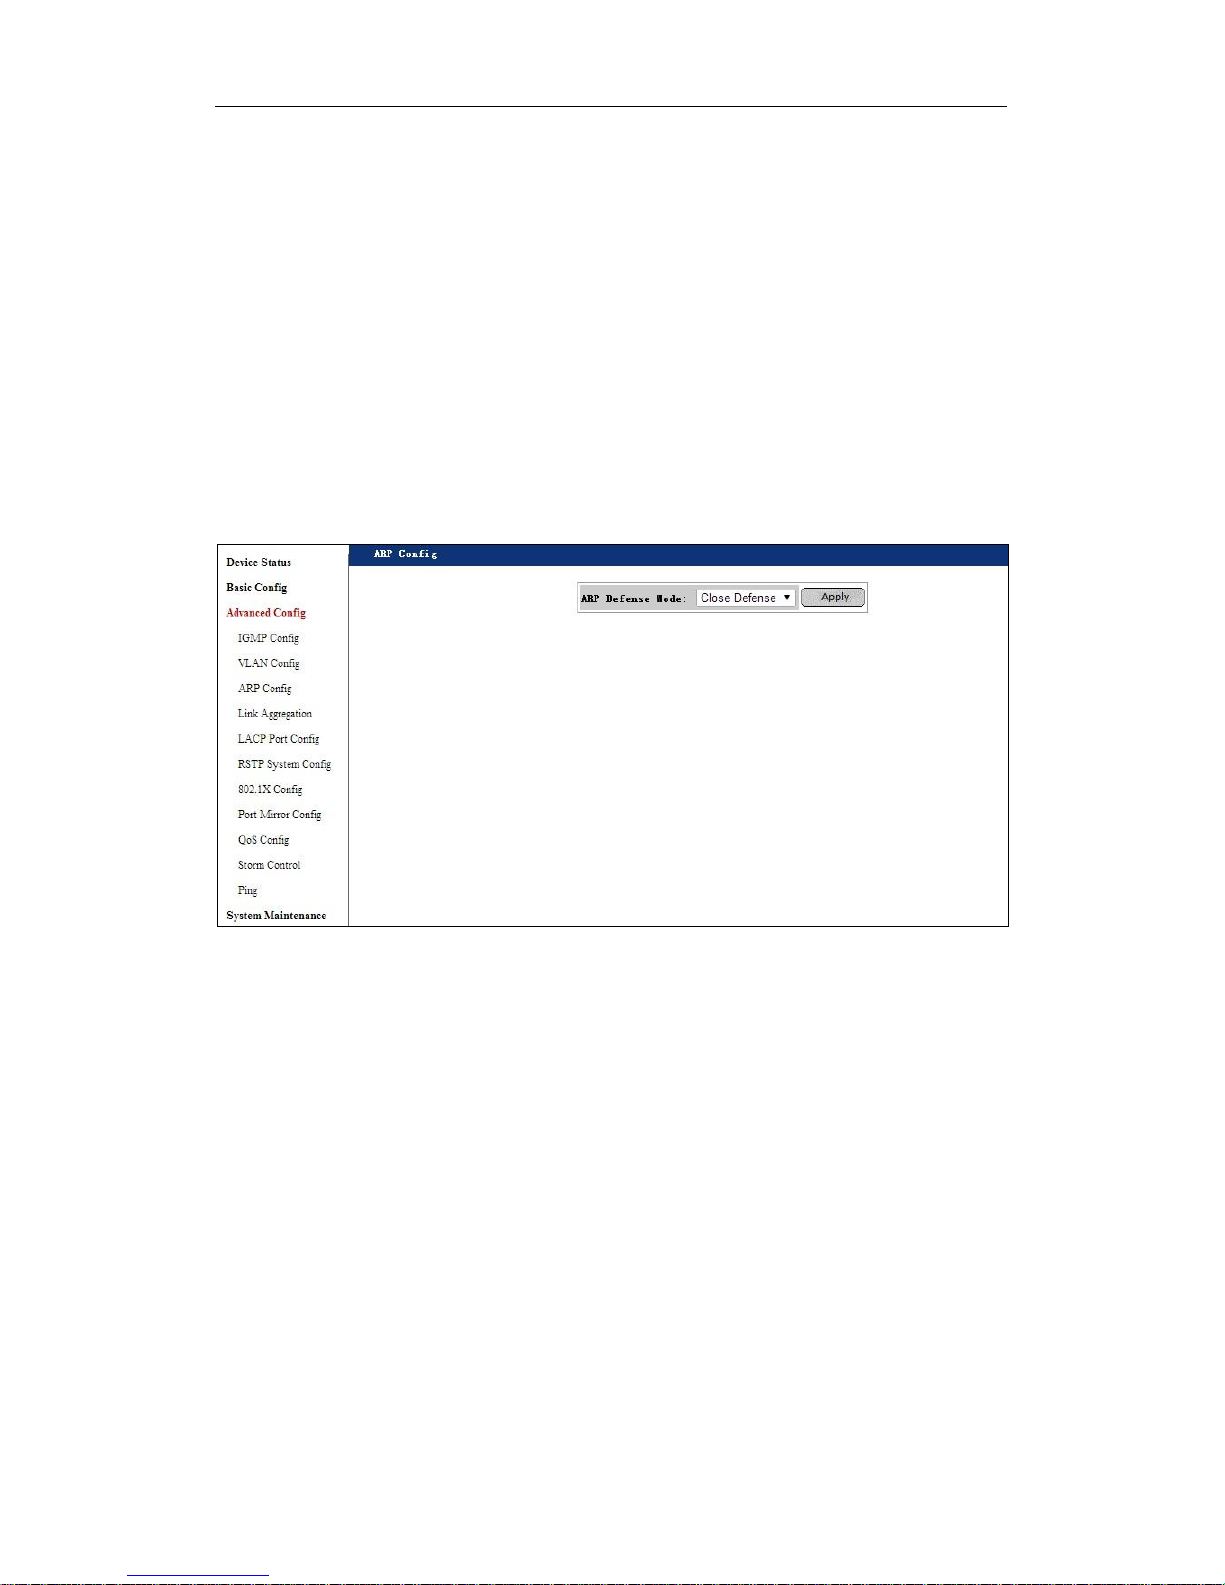
other, PC2 and PC4 can access each other;PC1 and PC4 can’t access each other, PC2 and
PC3 can’t access each other. The networking as follows:
Switch A Operation Steps:
Step One: Create a VLAN2 on Switch A, add both PC1 port(named as Port 1) and the port
connected to Switch B(named as Port 24) into VLAN2, then press”Application”.
Step Two: Create a VLAN3 on Switch A, add both PC2 port(named as Port 2) and the port
connected to Switch B(named as Port 24) into VLAN3, then press”Application”.
Step Three: Open VLAN property page of Switch A, configure the PVID of Port 1 as 2,
configure the PVID of Port 2(PC2 port) as 3, configure the PVID of Port 24(server port) as 1,
and check the “tag” item of Port 24.
Switch B Operation Steps:
Step One: Create a VLAN2 on Switch B, add both PC3 port(named as Port 1) and the port
connected to Switch A(named as Port 24) into VLAN2, then press”Application”.
Step Two: Create a VLAN3 on Switch B, add both PC4 port(named as Port 2) and the port
Page 22
User’s Guide
Page 22 of 54
connected to Switch A(named as Port 24) into VLAN3, then press”Application”.
Step Three: Open VLAN property page of Switch B, configure the PVID of Port 1 as 2,
configure the PVID of Port 2 as 3, configure the PVID of Port 24 as 1, and check the “tag”
item of Port 24.
Step Four: Test result is PC1 and PC3 can access to each other,PC2 and PC4 can access to
each other(configured to same VLAN); PC1 and PC4 can’t access to each other, PC2 and
PC3 can’t access to each other(configured to different VLAN, isolated).
To do some simple VLAN configuration, please press into “Fast configuration” to configure.
Notice: when entering into fast configuration page, the current VLAN configuration
information will be emptied.
4.3 ARP Config
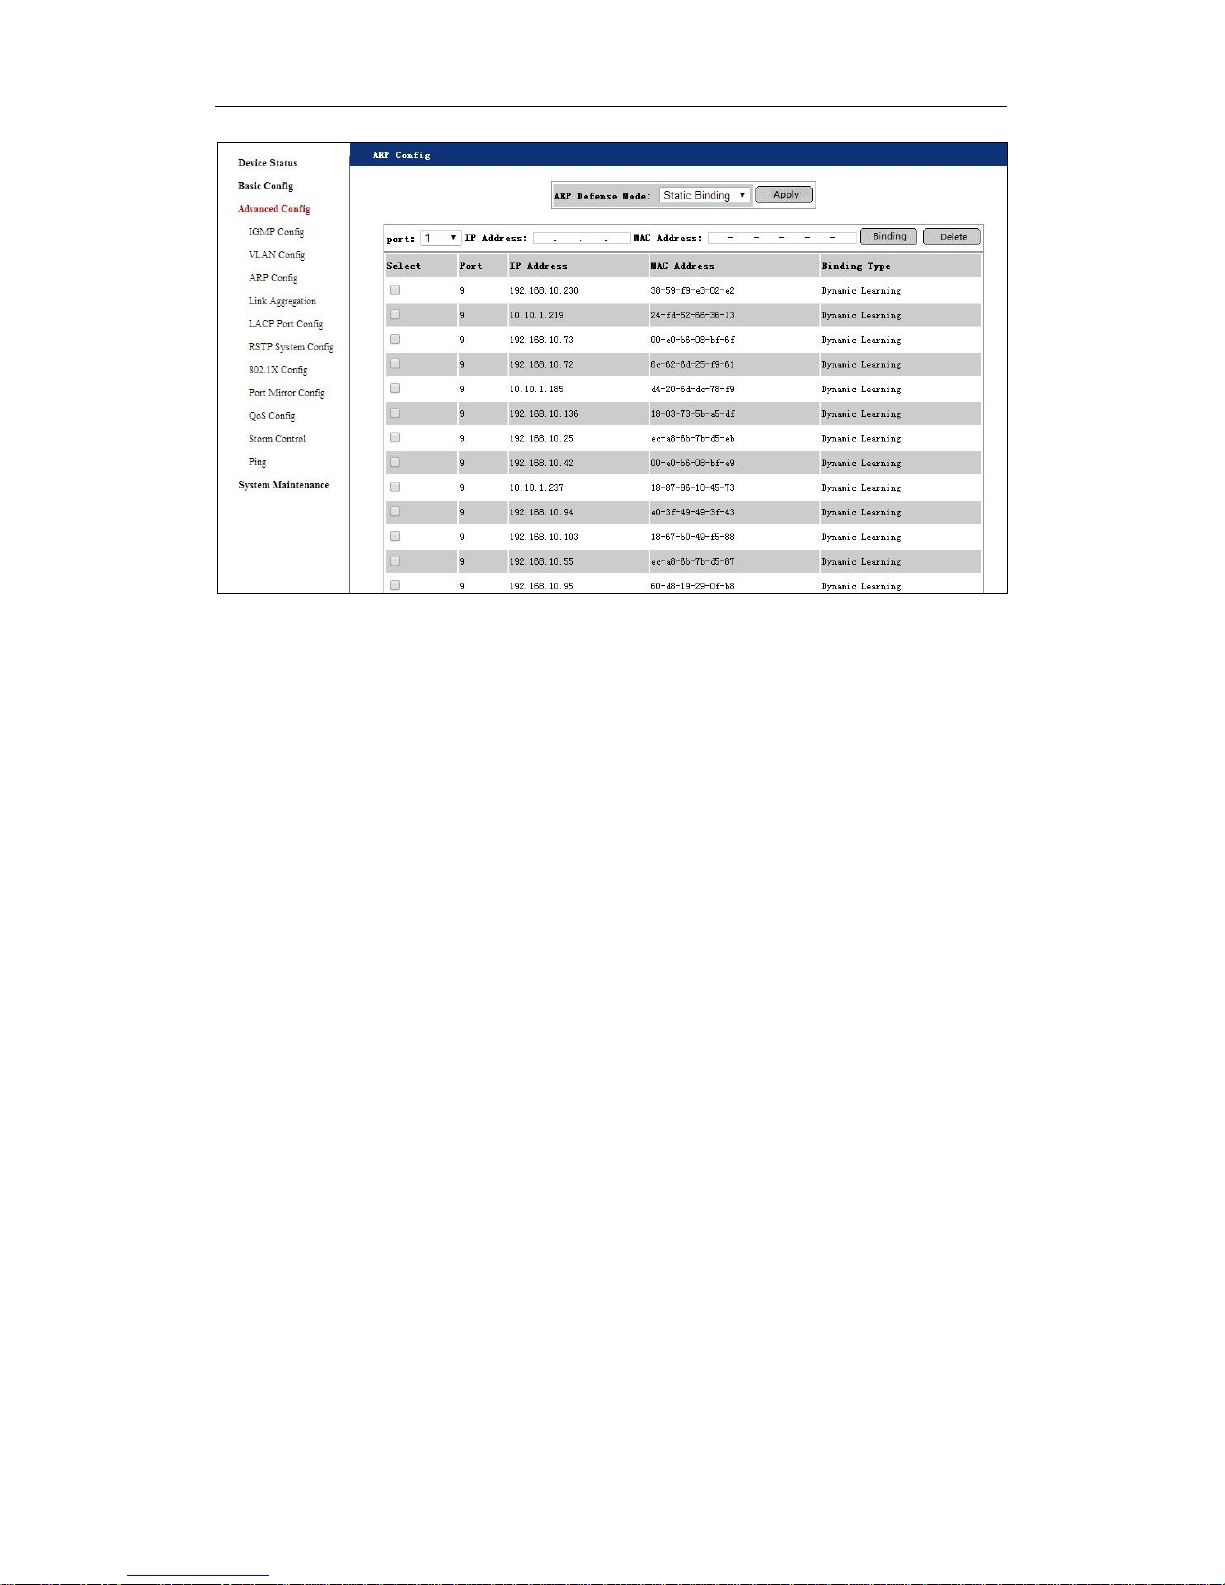
Picture 4.3.1 ARP config
The defaulted ARP defense mode is “Close Defence”, change to “Static Binding”, please click
“Apply” to confirm and enter into following page:
Page 23
User’s Guide
Page 23 of 54
Picture 4.3.2 Static Binding
First step configuration is adding ports, IP addresses and MAC address manually, then click
“Binding” botton to take effect or enter the ports,IP addresses and MAC addresses, then
press delete to take effect.
After first step configuration, the user can find port numbers, IP addresses, MAC addresses
and binding types in the middle check box, single or multiple items can be selected and then
binding or delete. The system supports maximum 128 binding items, max 32 items for each
port.
If a port is static binding, only the static ARP binding packets can be passed via this port.
Other IP and MAC information under this port only dynamic learning is allowed. If other ARP
information need to pass via this static binding port, must config the related other IP and MAC
information to static binding.
The ARP function also support defence against intranet address spoofing, effectively defense
against some DDos attacks, like syndemo attack. Choose to “Enable” and click “apply” to
take effect.The DDos Defense only take effect on the static binding ports and IP addresses.
Please note, the static binding ports will stop learning other ARP information once the DDos
Defense take effect. If new binding information need to be added, please first disable all port
static bindings or disable the DDos Defense function. Restart the DDos Defense function
after static binding of new ARP information.
Page 24
User’s Guide
Page 24 of 54
4.4 Link Aggregation
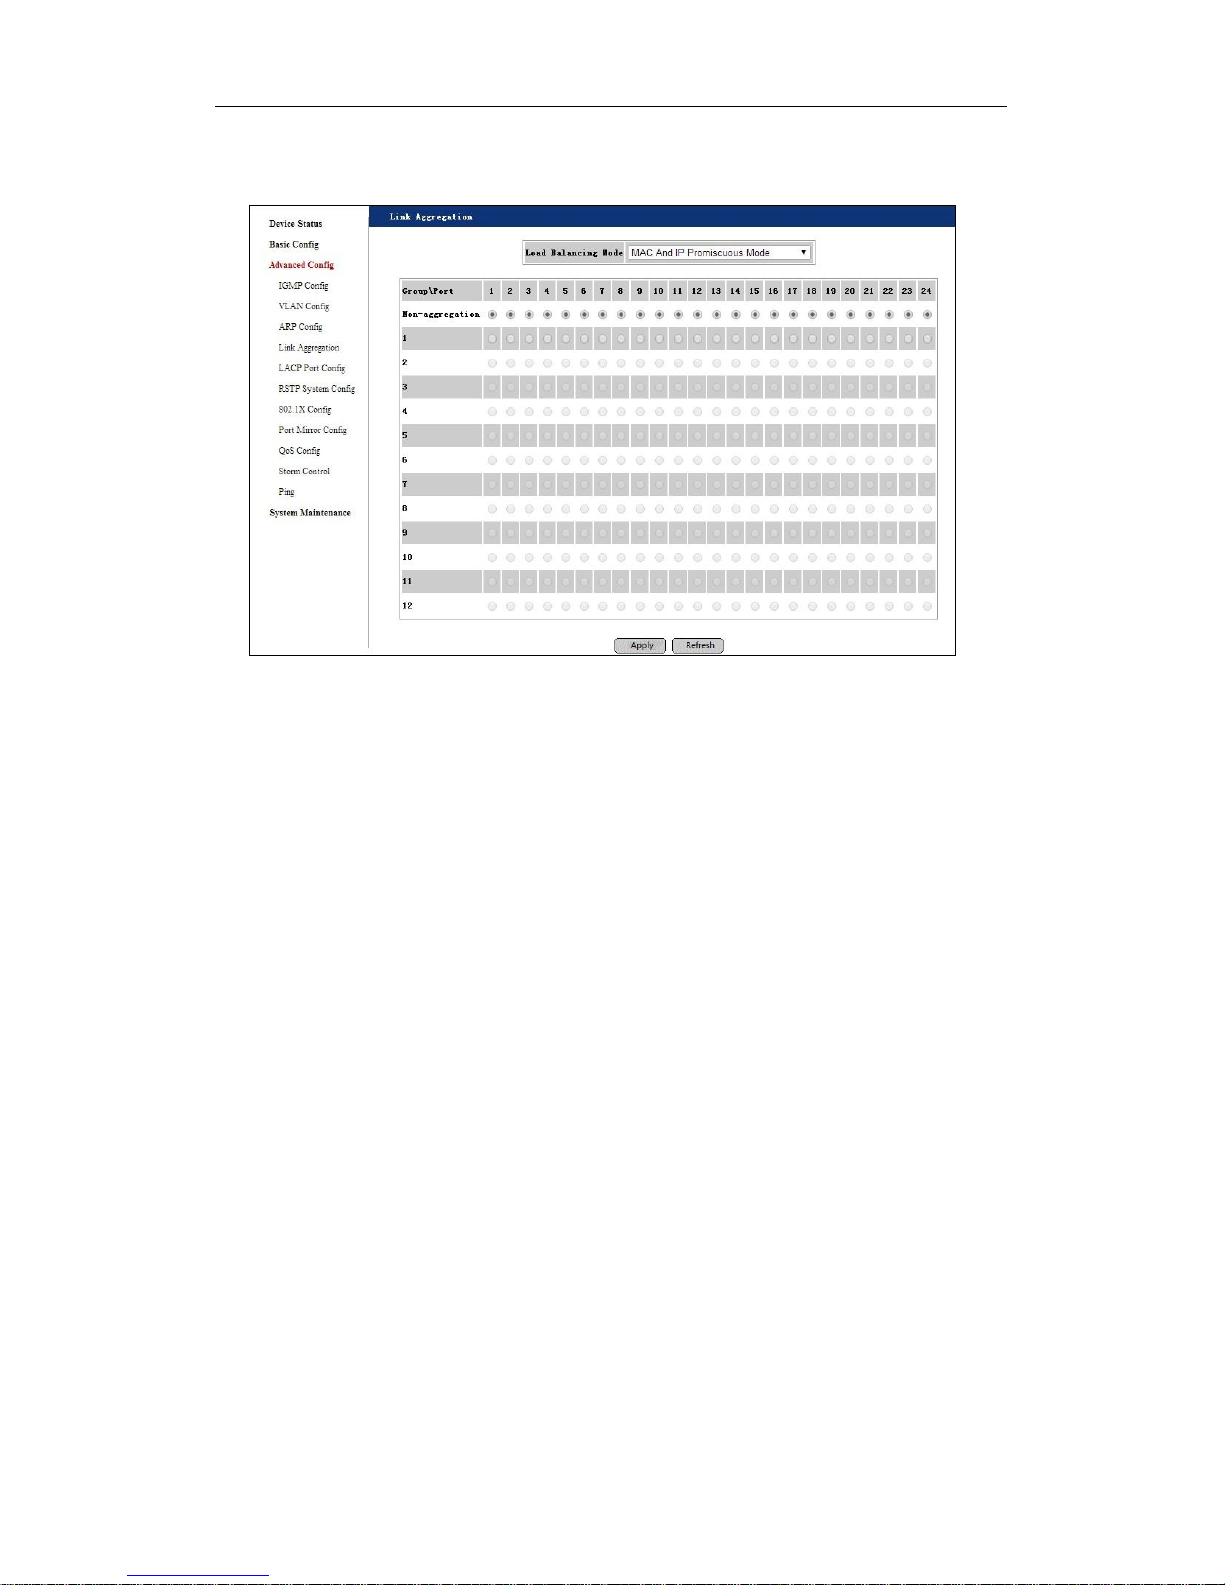
Picture 4.4.1 Link Aggregation
The load share method of link aggregation support different modes.
Source MAC address mode:it refers to share the data traffic according to the source MAC
address;
Destination MAC address mode: it shares the data traffic according to the destination MAC
address;
Source and Destination MAC address mode: it refers to share the data traffic according to
both source and destination MAC addresses;
Source and Destination IP address mode: it refers to share data traffic according to the
source and destination IP addresses;
Mixed MAC and IP mode: it refers to share data traffic according to both the MAC address
and IP address.
The load share method is a overall method, the system will keep the default “source and
destination IP mode” if there is no other special command.
There are 12 link aggregation groups listed in the “link aggregation” page. When there is no
link groups, Group1 can be configured and it will move to Group 2 when the configuration is
finished here. The switch supports maximum l12 ink aggregation groups and each group has
12 ports in maximum.
Page 25
User’s Guide
Page 25 of 54
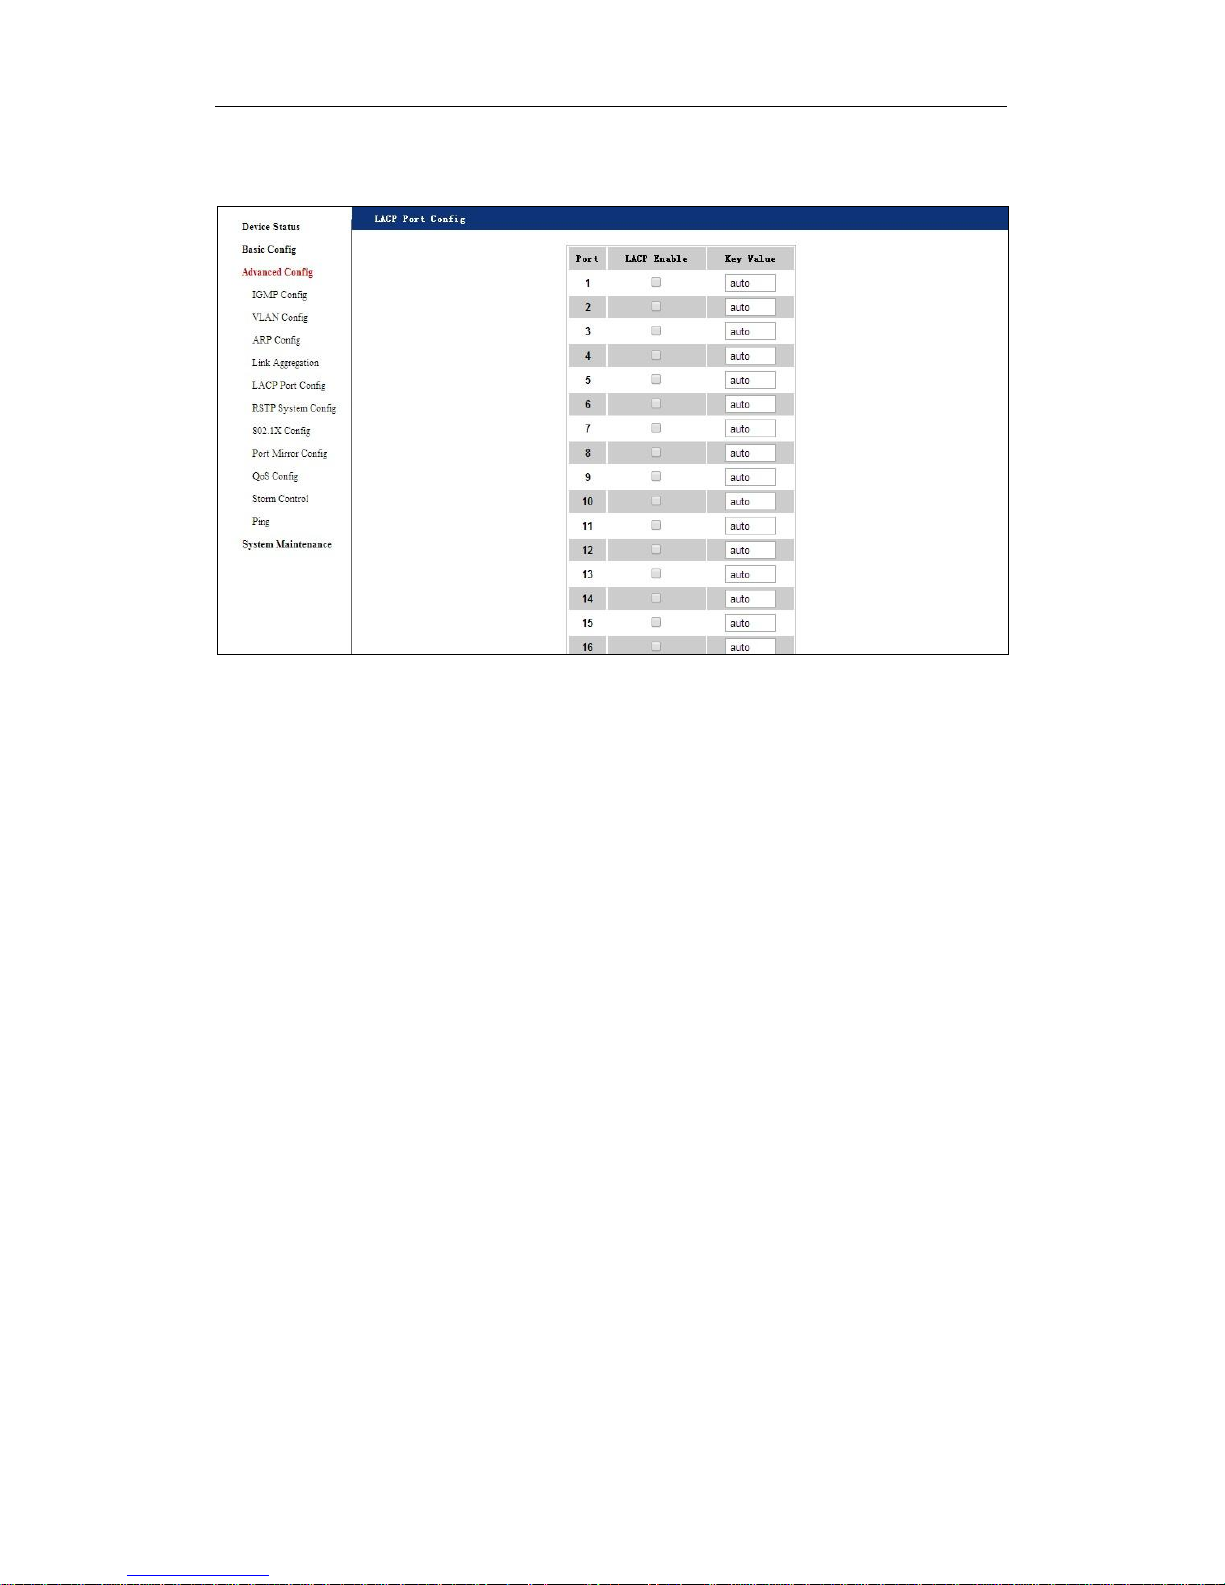
4.5 LACP Port Configuration
Picture 4.5.1 LACP Port Configuration
When the LACP protocol is on, the aggregated devices interactively gather information
through LACP. According to the parameters and status of each device, automatically receive
and dispatch Data of matchable link aggregation. When the Aggregation is formed, switches
keep in an aggregation link status, switches automatically adjusts link aggregation or
dissolute when configuration changes.
LACP configuration parameters include the protocol enable/disable status, negotiation key
and active-passive mode selection. Only when LACP is enabled, ports will be negotiated and
likely to form aggregated links. Key is the basis of Negotiation, only ports with the same key
will negotiate and possible to form a link aggregation.
If the port is configured as static aggregation, the dynamic LACP and KEY function are not
available. In contrary, if the port is configured as LACP on,then the static aggregation
functions are not available.
The dynamic LACP is advised to be used when connected with a server, and the server need
to support double nic aggregation function.
Page 26
User’s Guide
Page 26 of 54
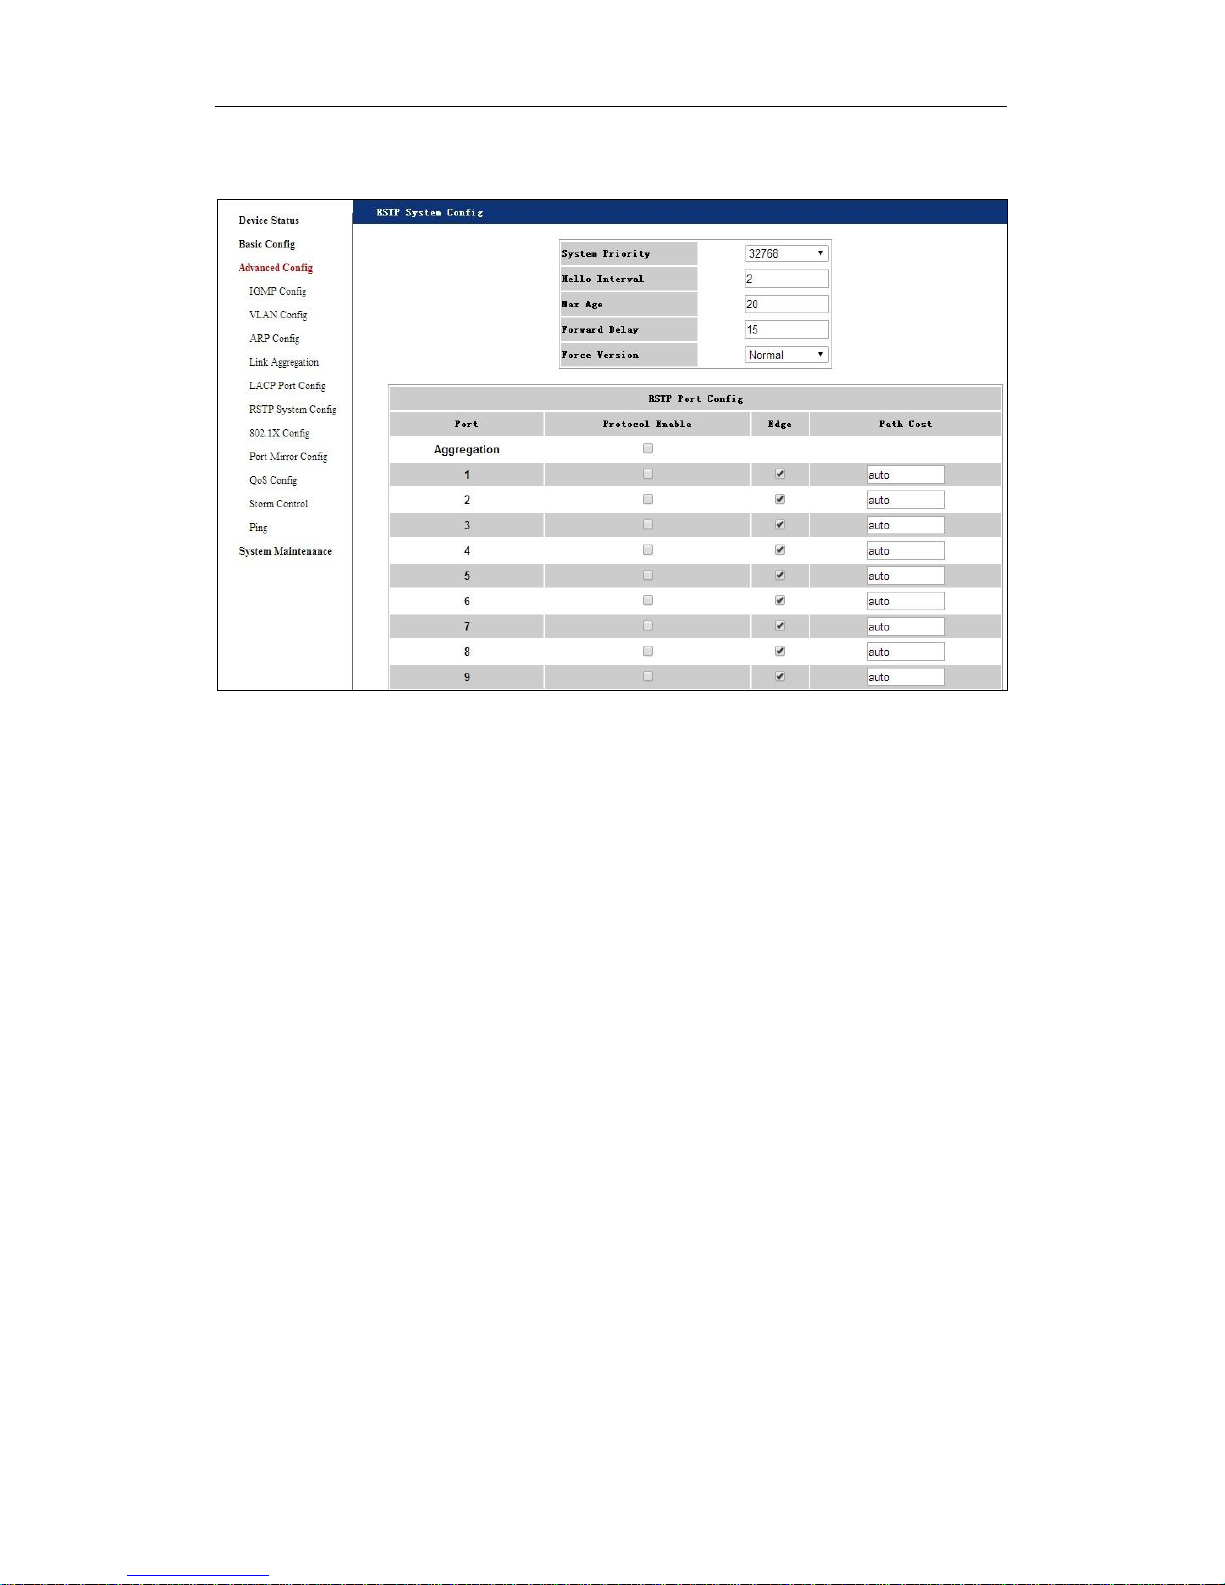
4.6 LACP Port Configuration
Picture 4.6.1 RSTP System Configuration
Above the page for Rapid Spanning Tree Protocol(RSTP) configuration. The “Edge” is
chosen when the switch is connected with a PC or other networking devices without RSTP
function. When “Edge” item is on, the port will enter into automatic forwarding state, will not
participate in RSTP logical topology calculations.
The default “Force Version” is Nomal, in this default configuration, the switch can recognize
both STP and RSTP format BPDU and forward the BPDU; When there are both STP and
RSTP end devices connected with the S3100 switch, the port need to do frequent switchings
between RSTP and STP, which is not good for stable network connection. User can configure
Force Version as “Compatible” to keep the system compatible with STP only.
Notice: In practical applications, to use one spanning tree for several VLANs is not
necessary, there is no communication between VLANs, so when RSTP is enabled,
Switch should be set to be only one VLAN. This is an improved RSTP, but not MSTP.
Page 27
User’s Guide
Page 27 of 54
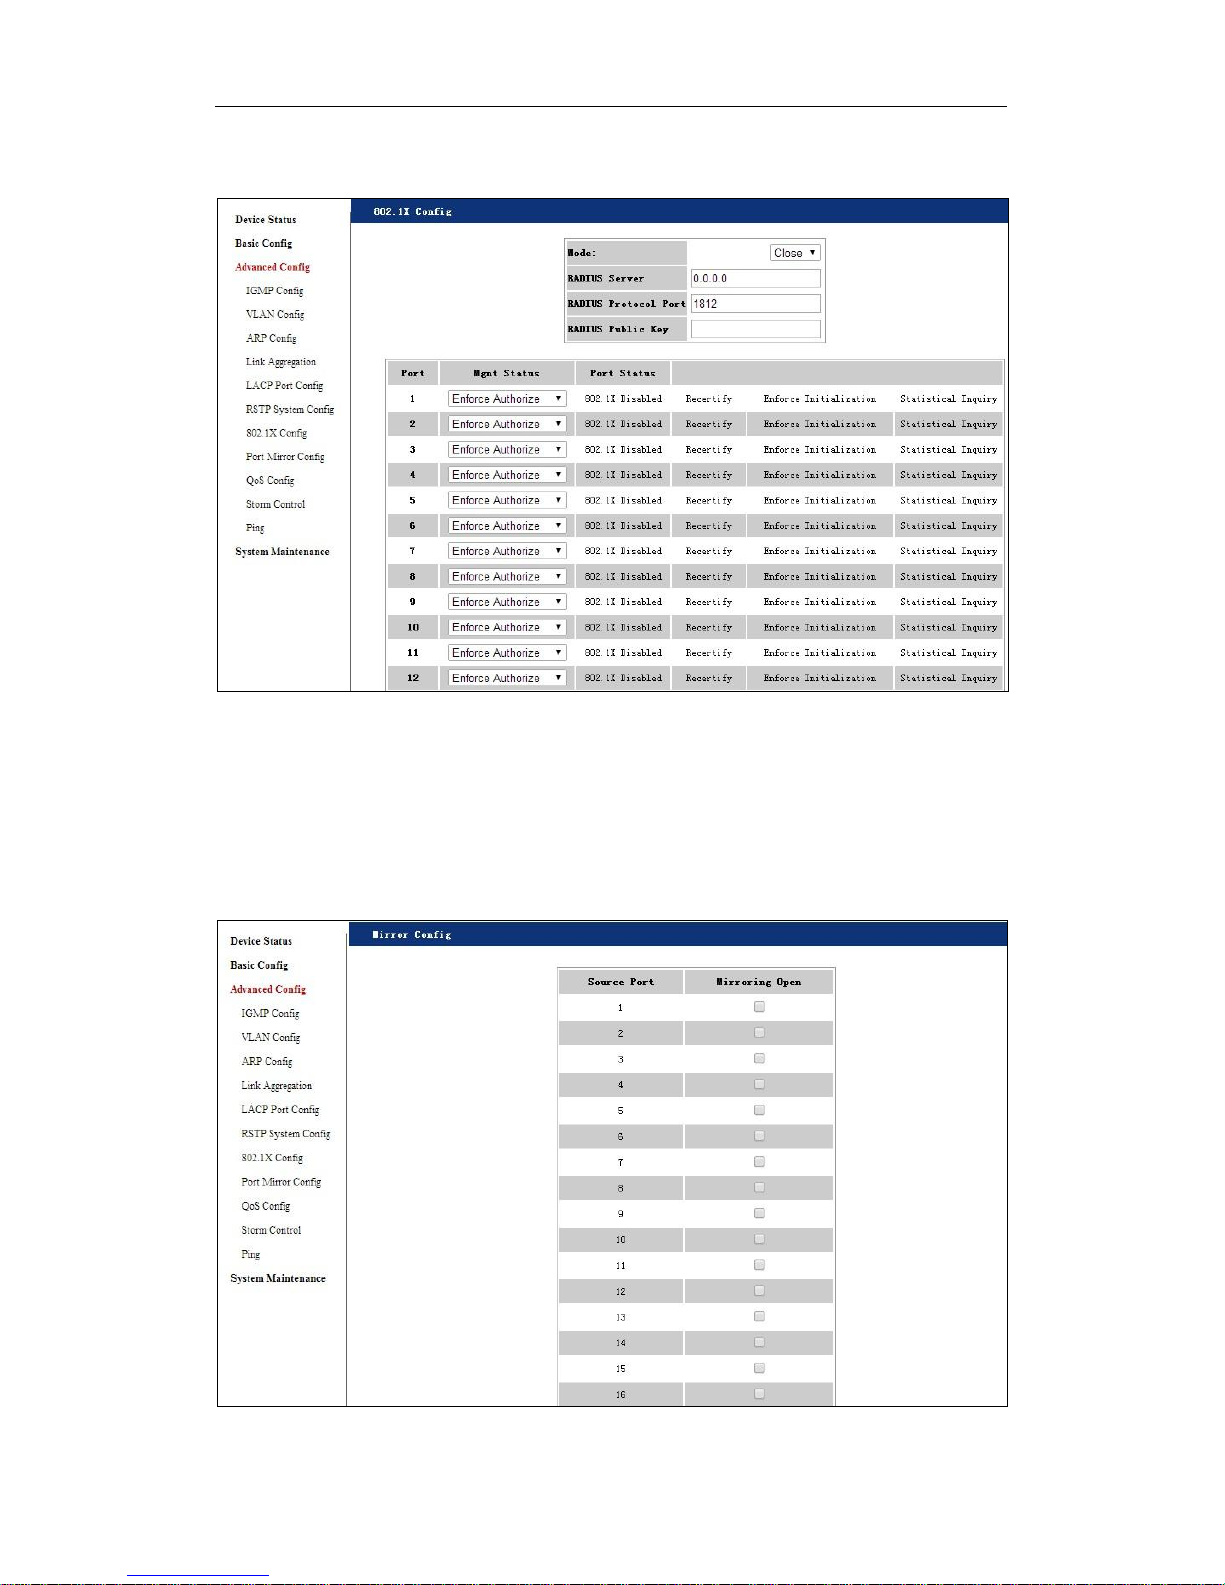
4.7 802.1X Configuration
Picture 4.7.1 802.1x configuration
The switch complies with port-based 802.1x certification. You can configure 802.1x server IP,
port number and key detailsf.
And you can modify certification status for each port,eg, Enforce Authrized, Port Status,
Recertify,Enforce Initialization, Statistical Inquiry
4.8 Port Mirroring Configuration
Picture 4.8.1 Port Mirroring Configuration
Page 28
User’s Guide
Page 28 of 54
Port mirroring is used on a network switch to send a copy of network packets or data traffic
from some ports (or an entire VLAN) to a network monitoring connection on specified switch
port. The original port is called Source Port, and the specified port is Mirroring Port. This is
commonly used for network appliances that require monitoring of network traffic without
influencing the normal working of every port, it’s a convenient onling-monitoring function.
All ports have mirroring function, but only one port can be configured as Mirroing Port in the
same system, but more than one Source Ports can be configured in the same system.
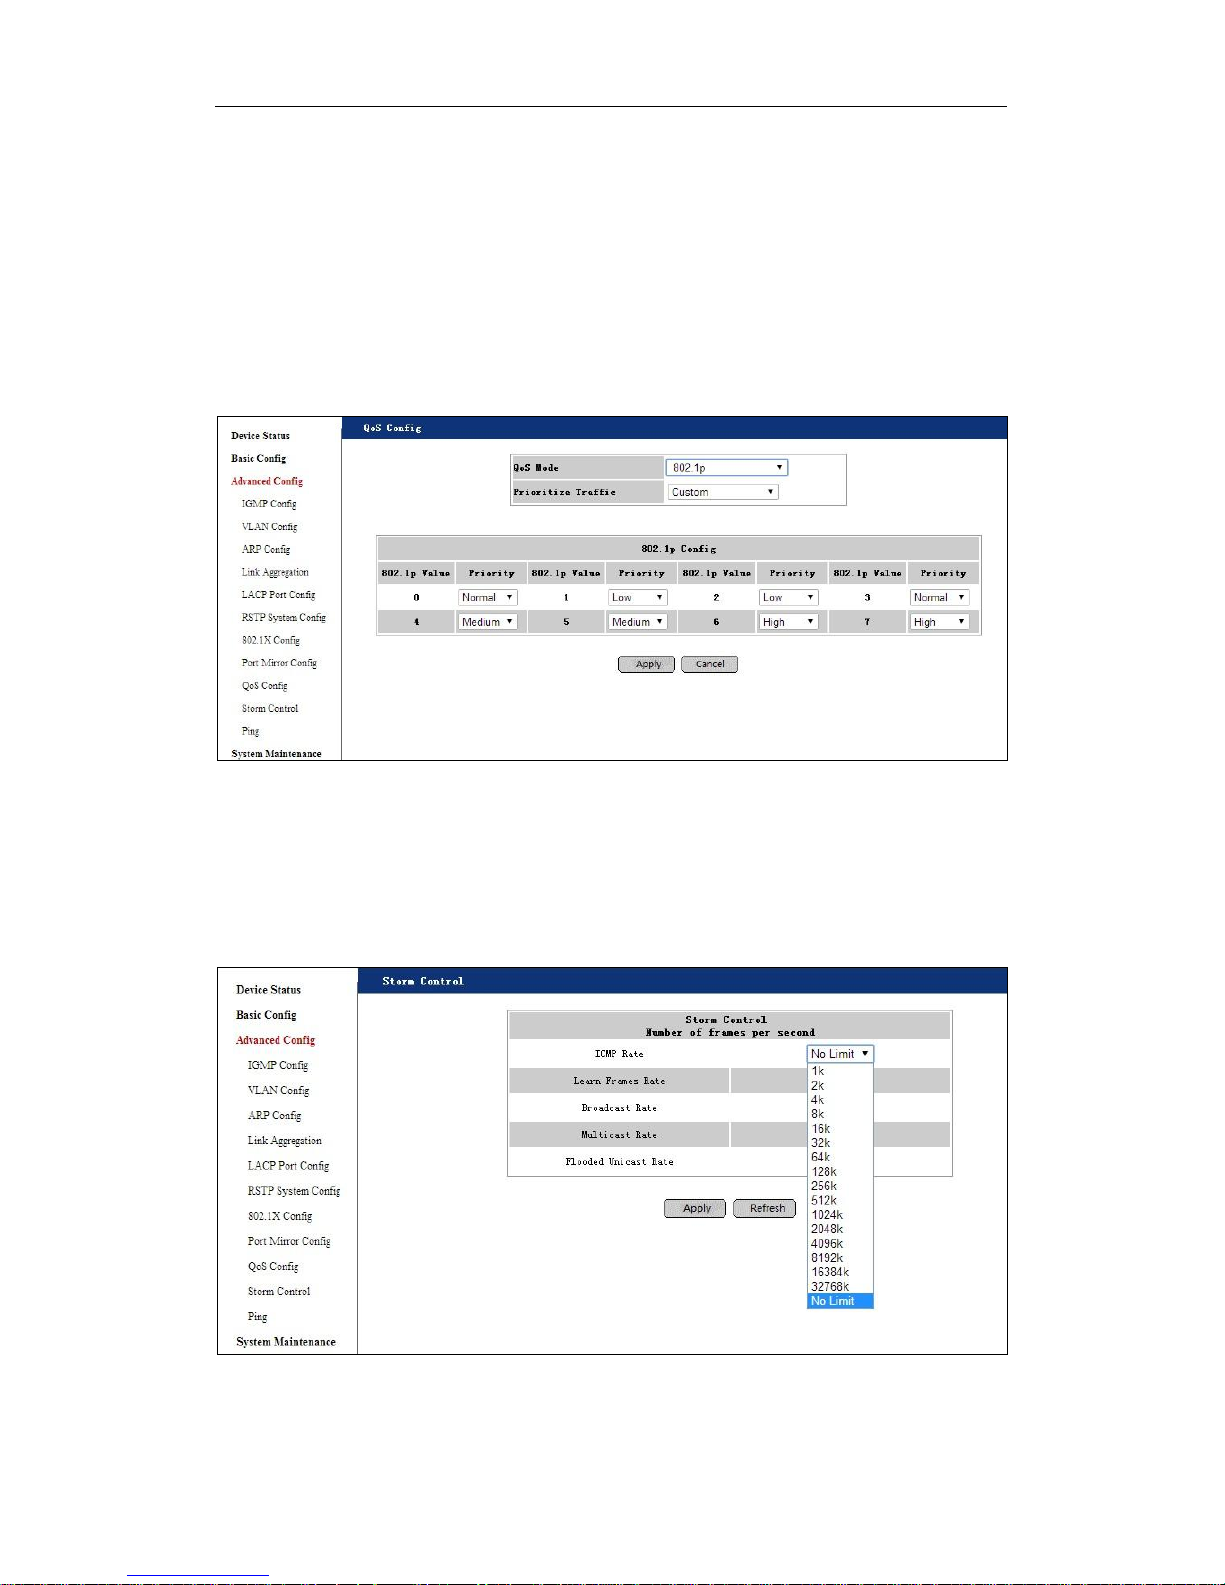
4.9 Qos Configuration
Picture 4.9.1 QoS Configuration
The default QoS mode is disabled. Other modes can be configured from the pull list, like
802.1P and DSCP. User can configure priority class in the configuration, packets with higer
priority class will be handled earlier.
4.10 Storm Control
Picture 4.10.1 Storm Control
The switch supports multiple storm control modes: IGMP traffic control, packet uploading rate
control, broadcast control, multicast control and unknown unicast control. Unknown unicast is
Page 29
User’s Guide
Page 29 of 54
the packet failed to find destination address, the switch will forward unknown unicast to all
ports, which will cause network conflicts.
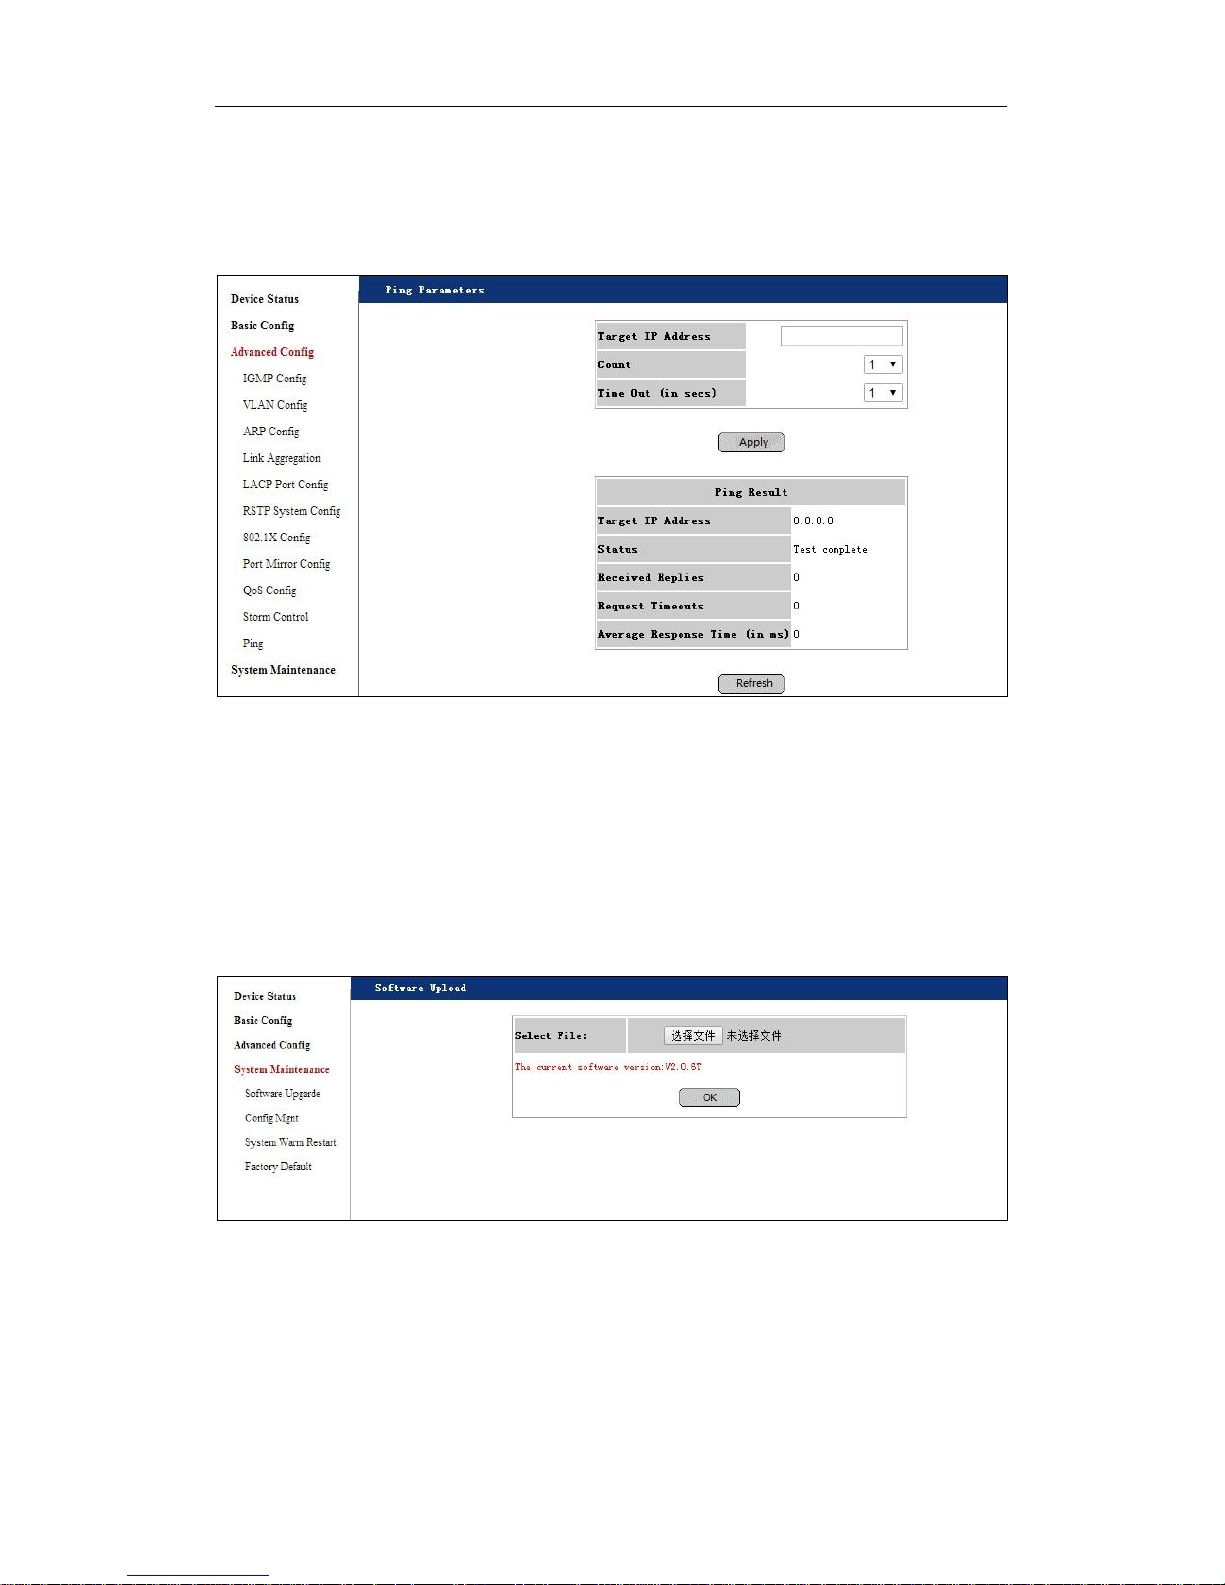
4.11 PING
Picture 4.11.1 Ping Test
Ping test is to check if a specified Client can be reached, the function is the same with ping
command under windows command lines. The IP addresses of switch and PC must be in
same network segment.
Chapter 5 System Configuration
5.1 Software Upgrade
Picture 5.1.1 Software Upgrade
The user can upgrade the software in this page, the current system software version number
is showed in this page. Latest software version can be download from the website.
Page 30
User’s Guide
Page 30 of 54
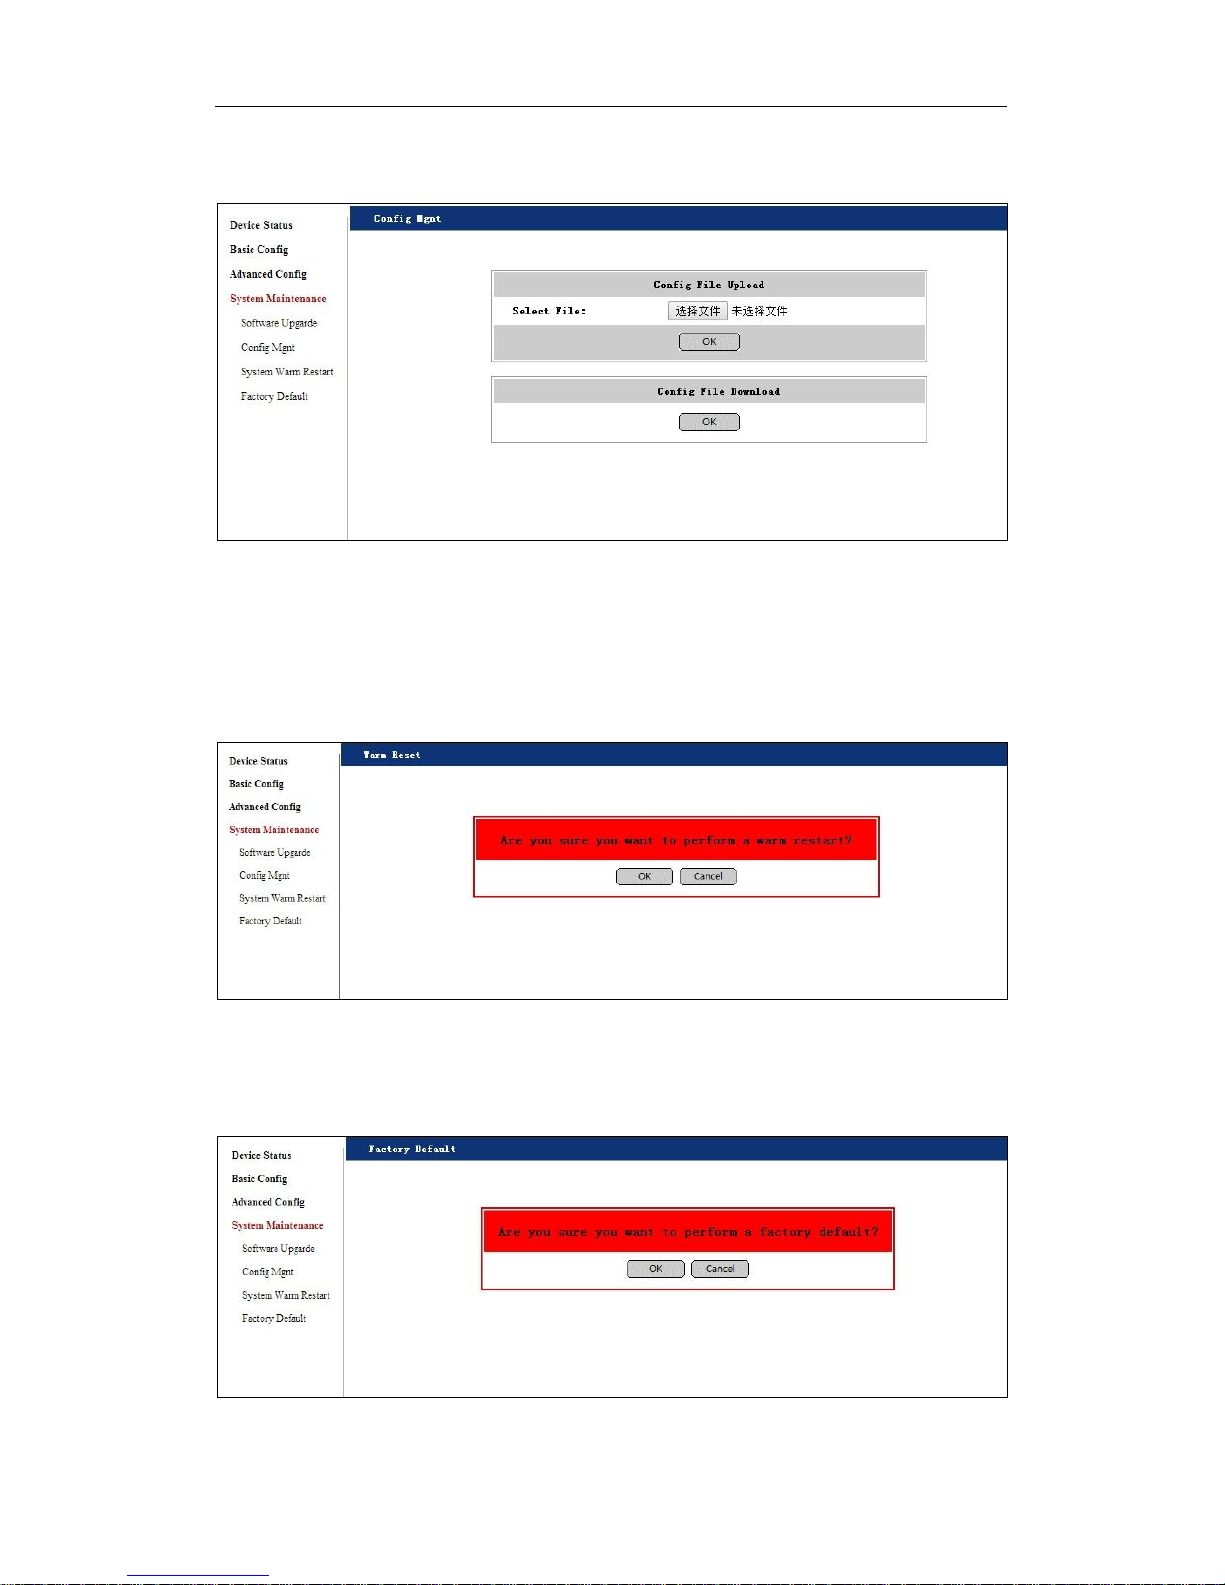
5.2 Configuration Management
Picture 5.2.1 Configuration Management
The user can upload or download the system configuration files in this page to bakup or
recover the system configuration.(Notice:the download configuration files don’t include IP
address information. The upload configuration file won’t cover the current IP address.)
5.3 System Warm Reset
Picture 5.3.1 System Warm Reset
Warm reset needed when the user modify some system information like the MAC address.
5.4 Factory Reset
Picture 5.4.1 Factory Reset
Page 31
User’s Guide
Page 31 of 54
The switch support factory reset, reset information includes all configurations, IP addresses
and password.
If the login IP address and password are missed, the user can do factory reset via CLI
command or connecting two specified ports from a device. Please follow the below steps to
connect ports and reset to default setting.
Step One: connect Port No. 9 and No.16 of the switch.
Step Two: Cut off the power supply and reboot device after 10 seconds.
Step Three: Port No. 9 and No.16 will flash when rebooting the device, reboot is finished
when the flashing stops. Disconnect Port No. 9 and No.16 after all system indicators light on,
and the factory reset is finished.
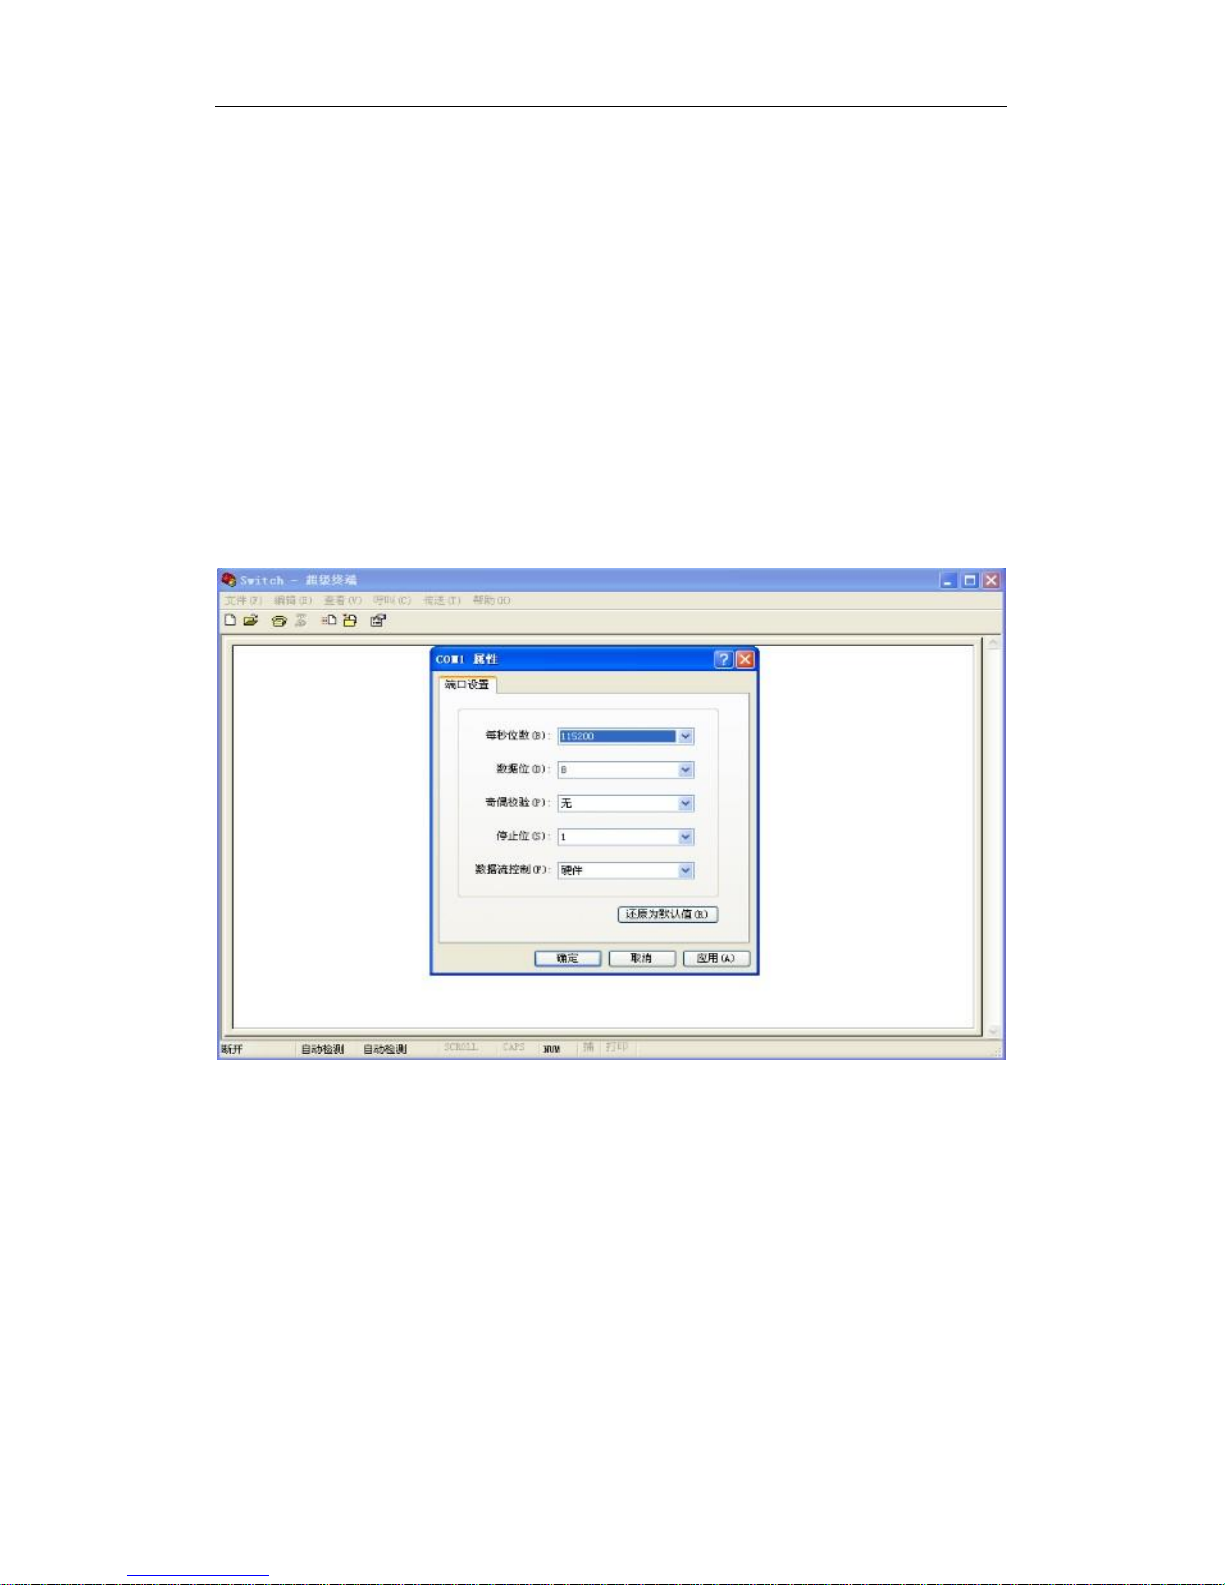
Part Three CLI Configuration Guide
Picture 3.0.1 Hyper Terminal Configuration
When manage the switch by Console port, the above page will be showed. Please configure
“COM1” according to the port number of PC, then click “Application” to enter into below
operation page.
Page 32
User’s Guide
Page 32 of 54
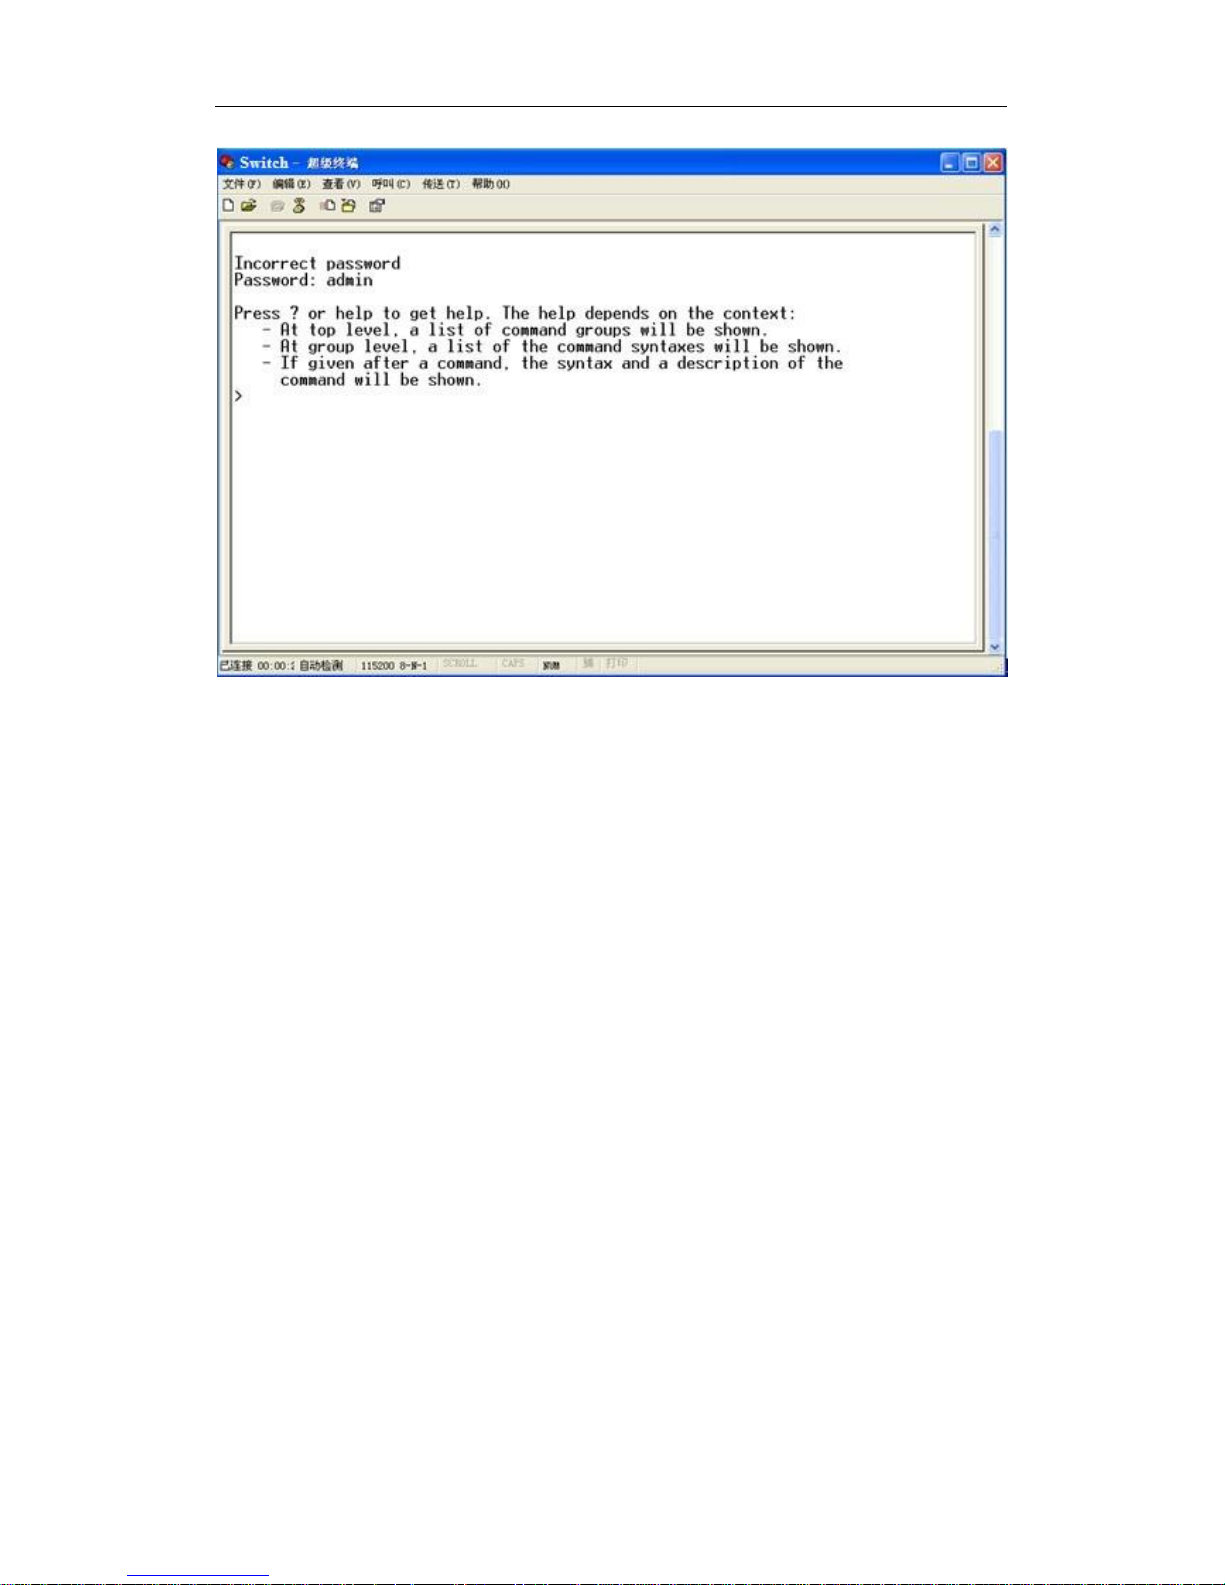
Picture 3.1.1 Login Page
Please refer to the above CONSOLE login page.
Default password: admin
Help command: “?”
Main Commands include:
System -system configuration
Console -console parameter configuration
Port -port configuration
MAC - MAC configuration
VLAN - VLAN configuration
ARP - ARP configuration
Aggr -Link aggregation configuration
LACP - LACPconfiguration
RSTP -RSTP configuration
User Group -user group configuration
QoS - QoS configuration
Mirror -port mirroring configuration
IP - IP address configuration
Dot1x - Dot1x configuration
IGMP - IGMP configuration
Debug -debug command won’t be introduced in this manual
Please enter into the above command words to enter into related command configuration
mode. Example, enter “system” to enter into system command configuration. If you need to
enter into another command configuration, please exit from the current configuration.
Page 33
User’s Guide
Page 33 of 54
Back to previous mode: “/”
Page 34
User’s Guide
Page 34 of 54
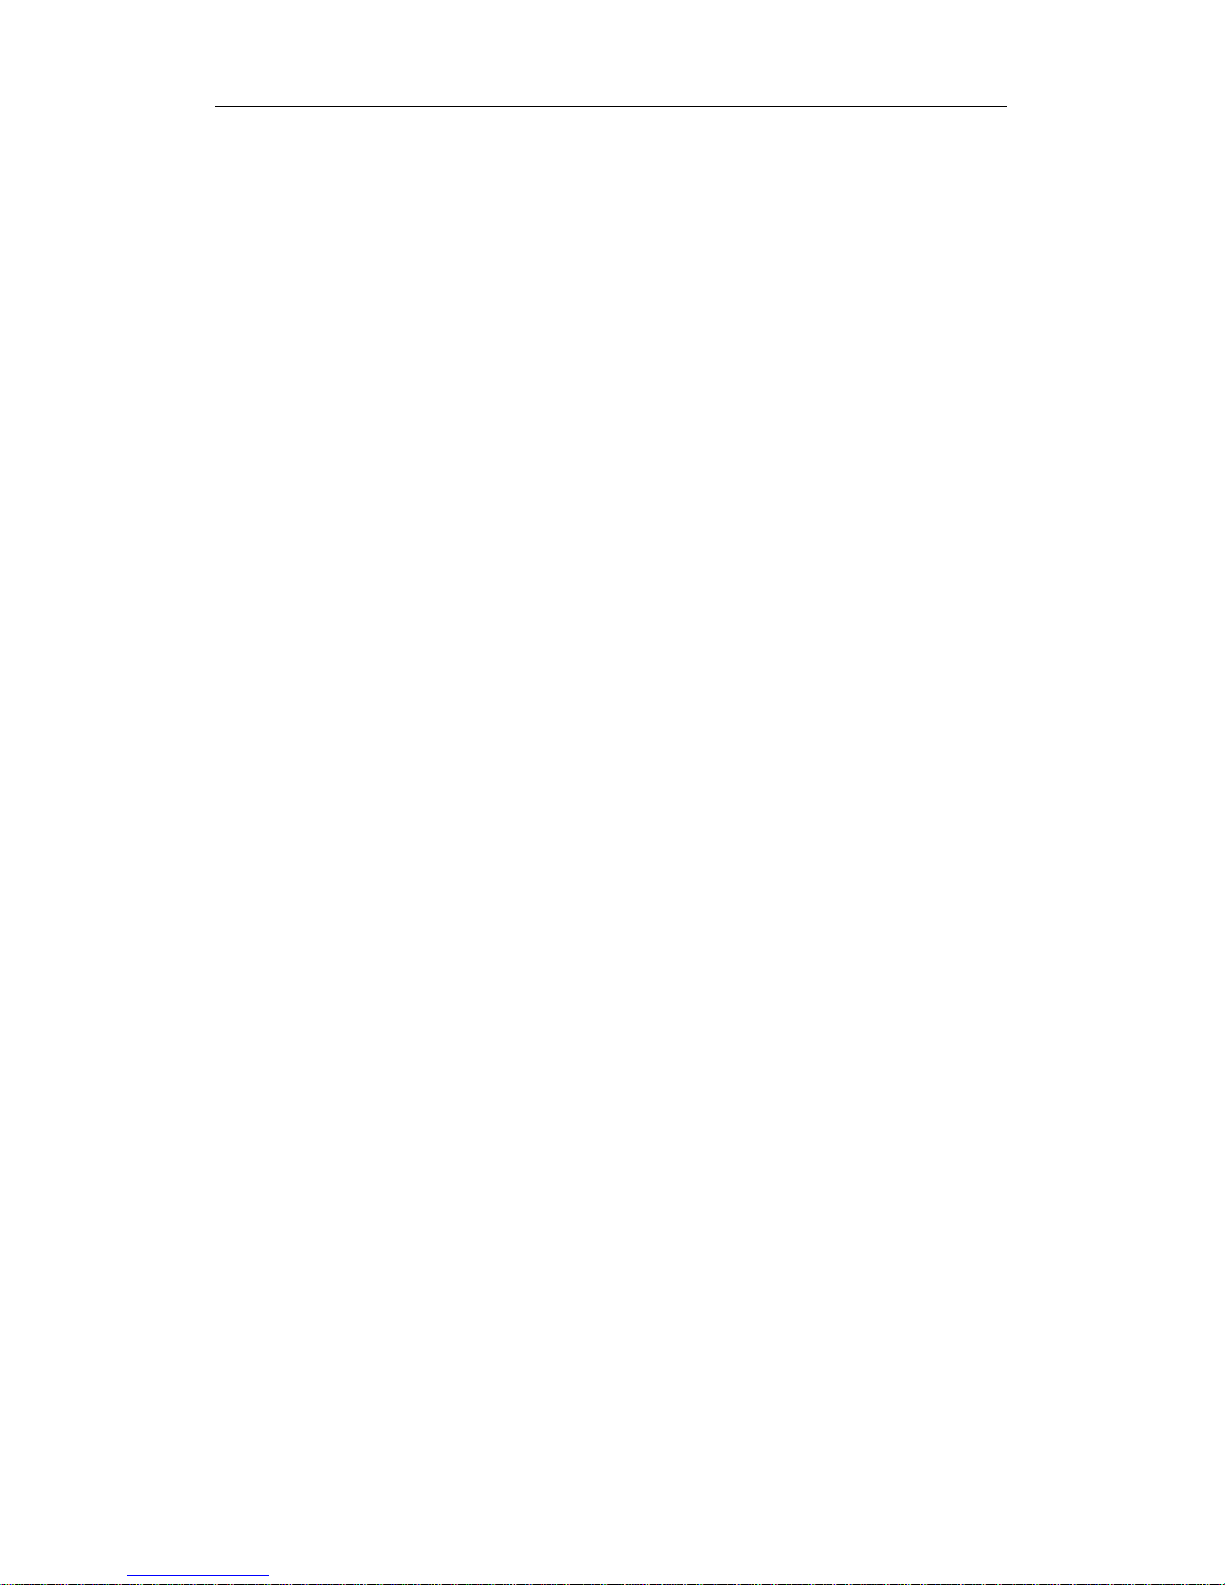
Chapter 1 System Configuration
Enter “system” command to get the system configuration page, as below picture.
Picture 3.1.3 System Configuration
1. Query system configuration
Command: configuration[all]
[all] is a optional parameter, enter a parameter to query system configuration
2. Restore default configuration
Command: restore default [keepIP]
[keepIP] is optional parameter, enter this parameter to keep the current IP configuration
Description: to restore system default configuration
3. System Renaming
Command: Name [<name>]
<name> refers to system name
4. System Reboot
Command: Reboot
Description: hot reboot the system
5. SNMP configuration
Command: SNMP [enable|disable]
Enable- to switch on SNMP function
Disable-to switch off SNMP function
Description: default to disable
6. SNMP agent address
Command: Trap [<IP Address>]
<IP Address> - refers to IP address of SNMP agent
Description: configure the default receiving IP address of SNMP trap packets.
7. SNMP reading pemission password
Page 35
User’s Guide
Page 35 of 54
Command: Readcommunity [<community string>]
<community string> - reading permission password
Description: configure the reading permission password of SNMP
8. SNMP writng permission password
Command: Writecommunity [<community string>]
<community string> - reading permission password
Description: configure the writing permission password of SNMP
9. SNMP trap password
Command: Trapcommunity [<community string>]
<community string> - trap password
Description: configure the trap password of SNMP
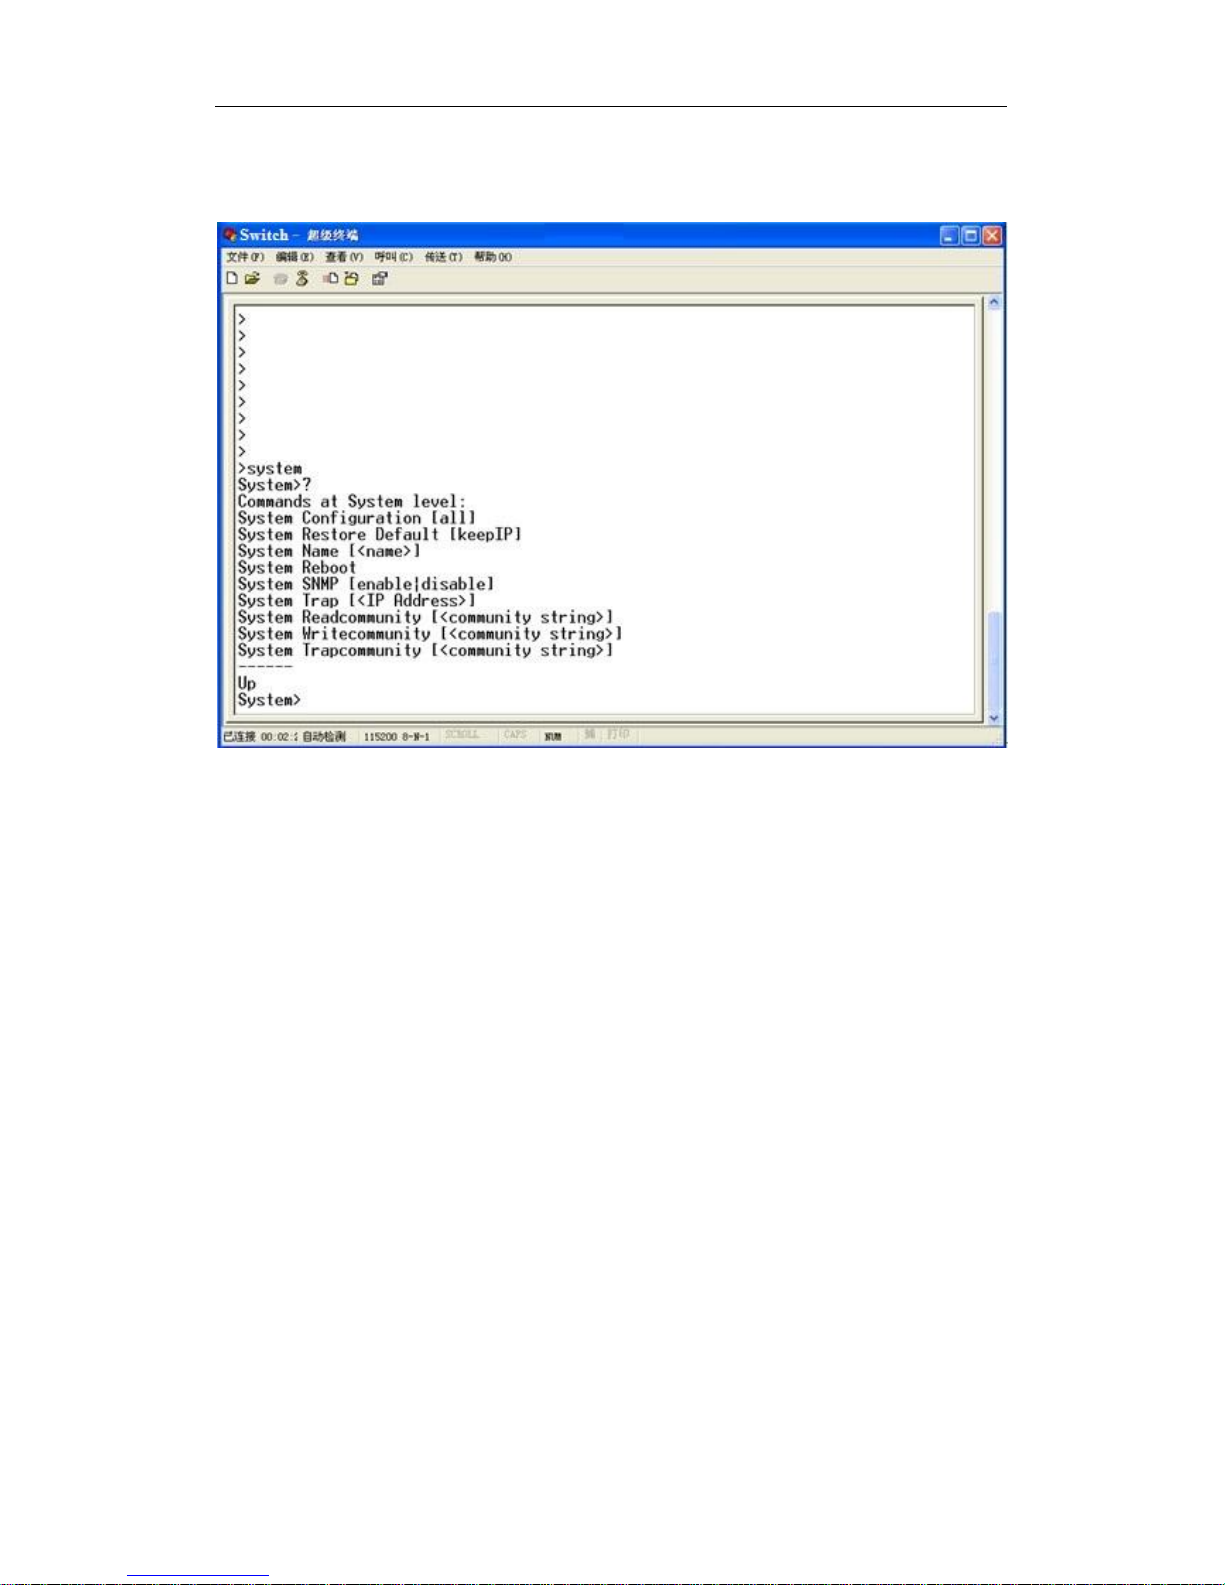
Chapter 2 Console Parameter Configuration
Please input “ console” command to enter into console configuration, as below picture:
Picture 3.1.2 Console Parameter Configuration
1. Command: configuration
Description: display the current console configuration, including password, command
prompt and timeout.
2. CONSOLE login password
Command:Password [<password>]
<password> -login password
Description: configure console login password, the default is admin.
3. CONSOLE timeout
Command: Timeout [<timeout>]
<timeout>-time out limits, the units is second.
Description:Console timeout default is 0 second.
Page 36
User’s Guide
Page 36 of 54
4. Configure console prompt
Command: Console Prompt [<prompt string>]
<prompt string>-console prompt, maximum 10 english words
Description: configure console prompt
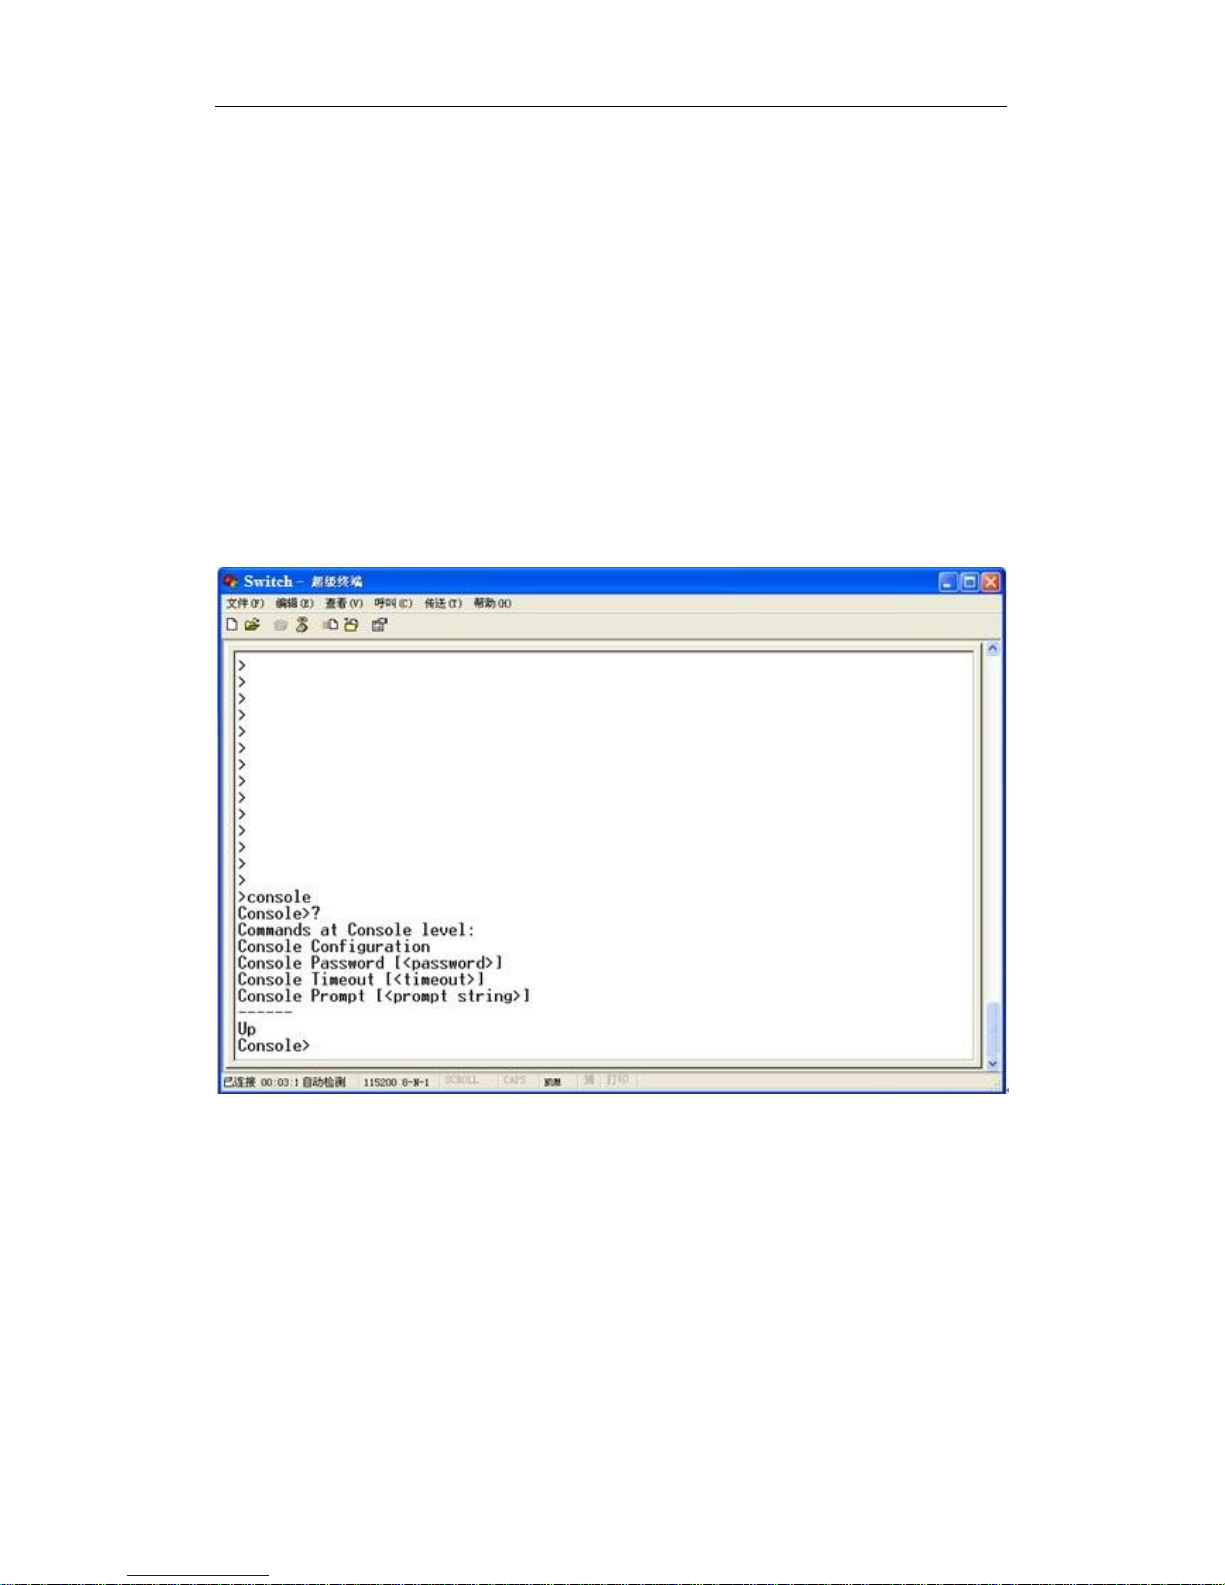
Chapter 3 Port Configuration
Input “ port” command to enter into port configuration, as below picture:
Picture: 3.1.3 Port Configuration
1. Query port configuration
Command: Configuration [<portlist>]
<portlist>-port number list, 1,2,4-5 for option
Description: Query the port configuration information
2. Port working mode
Command: Mode [<portlist>] [<mode>]
<portlist>-Port number list,1,2,4-5 for option
<mode>-port working mode, includes below parameters:
Auto- auto negotiation
10hdx- 10M half duplex
10fdx- 10M full duplex
100 hdx- 100M half duplex
100fdx- 100M full duplex
1000fdx- 1G full duplex
Description: static configuration of port working modes, the default is auto-negotiation.
3. Port flow control
Command:Flow Control [<portlist>] [enable|disable]
Page 37
User’s Guide
Page 37 of 54
<portlist>-port nubmer list, 1,2,4-5 for option
[enable|disable]-enable to switch on, disable to switch off.
Description:configure the pause traffic control function of ports, the default is disable.
4. Port State
Command:State [<portlist>] [enable|disable]
<portlist>-port nubmer list, 1,2,4-5 for option
[enable|disable]-enable to switch on, disable to switch off.
Description:configure the state of port forwarding function, the default state is enable.
5. Max Frame of single port
Command:MaxFrame[<portlist>] [<framesize>|reset]
<portlist>-port nubmer list, 1,2,4-5 for option
<framesize>-maximum frame size, the range is 1518~9600.
Reset-restore to default configuration of 1518
Description:configure the maximum frame size, the default is 1518.
6. Query port statistics
Command:Statistics [<portlist>] [clear]
<portlist>-port nubmer list, 1,2,4-5 for option
[clear]-reset statistics, for option.
Reset-restore to default configuration of 1518
Description:Query port statistics information
7. Flow control mode
Command:Excessive Collisions Drop [enable|disable]
Enable-flow control for lost packets
Disable-flow control for crowded packets
Description:Configure the flow control mode, the default config is lost packets flow control.
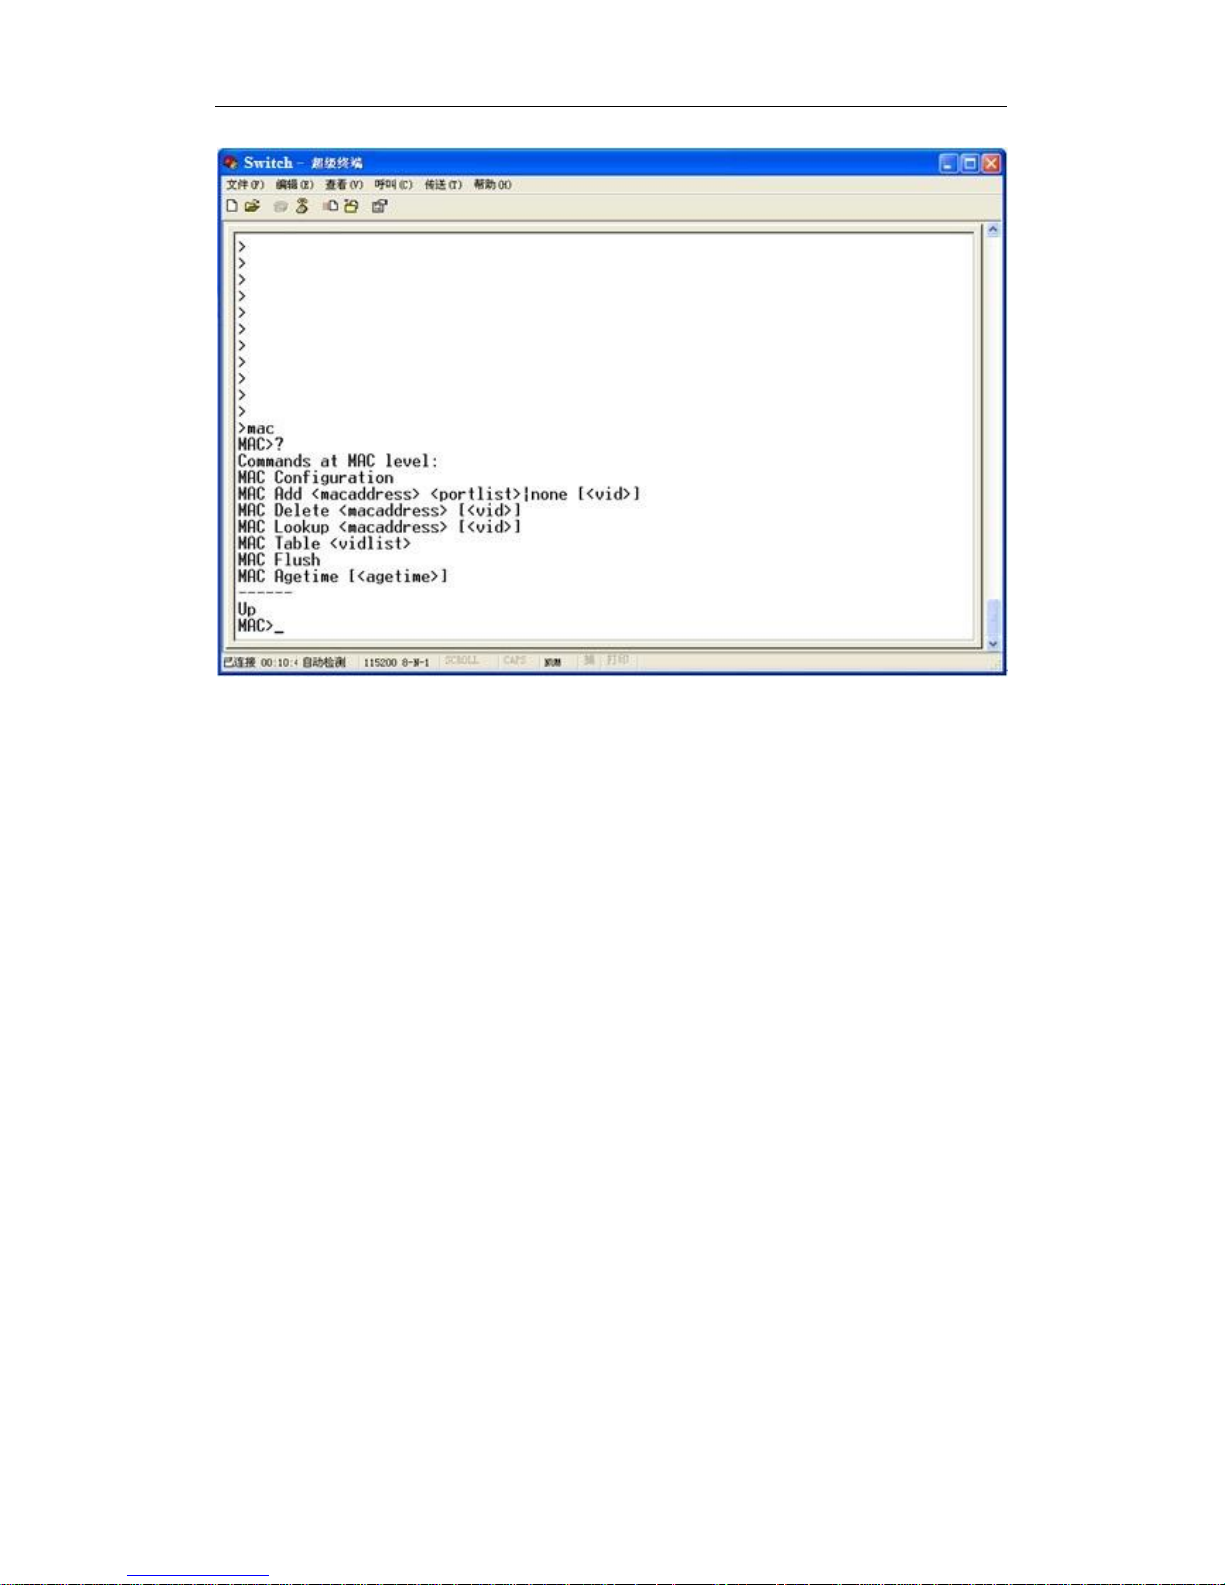
Chapter 4 MAC Configuration
Input “mac” command to enter into mac configuration mode, as below piture showed.
Page 38
User’s Guide
Page 38 of 54
Picture 3.1.4 MAC configuration
1. Query forwarding table configuration
Command: configuration
Description:query all forwarding address table configuration in layer 2.
2. Add new Layer 2 forwarding table
Command:Add <macaddress> <portlist>|none [<vid>]
<macaddress>-MAC address, e.g.:00:00:11:22:33:44
<portlist>|none-port list, like1,2,4-5,none refers to entire MAC address table.
Description:add new layer 2 forwarding table
3. Delete Layer 2 forwarding table
Command:Delete <macaddress> [<vid>]
<macaddress>-MAC address, e.g.:00:00:11:22:33:44
[<vid>]-VLAN ID number for option, default is 1
Description: delete layer 2 forwarding table
4. Query forwarding table
Command:Lookup <macaddress> [<vid>]
<macaddress>-MAC address, e.g.:00:00:11:22:33:44
[<vid>]-VLAN ID number for option, default is 1
Description: query the state of speicific layer 2 forwarding table
5. Query specified layer 2 VLAN forwarding table
Command:Table <vidlist>
<vidlist>-VLAN list, like 1,3,5-6
Description: query all the layer 2 forwarding table of specified VLAN
6. Aging time of forwarding table
Command:Agetime [<agetime>]
Page 39
User’s Guide
Page 39 of 54
[<agetime>] -age time, the unit is second, default setting is 300.
Description: configure the agetime of dynamic layer 2 forwarding table.
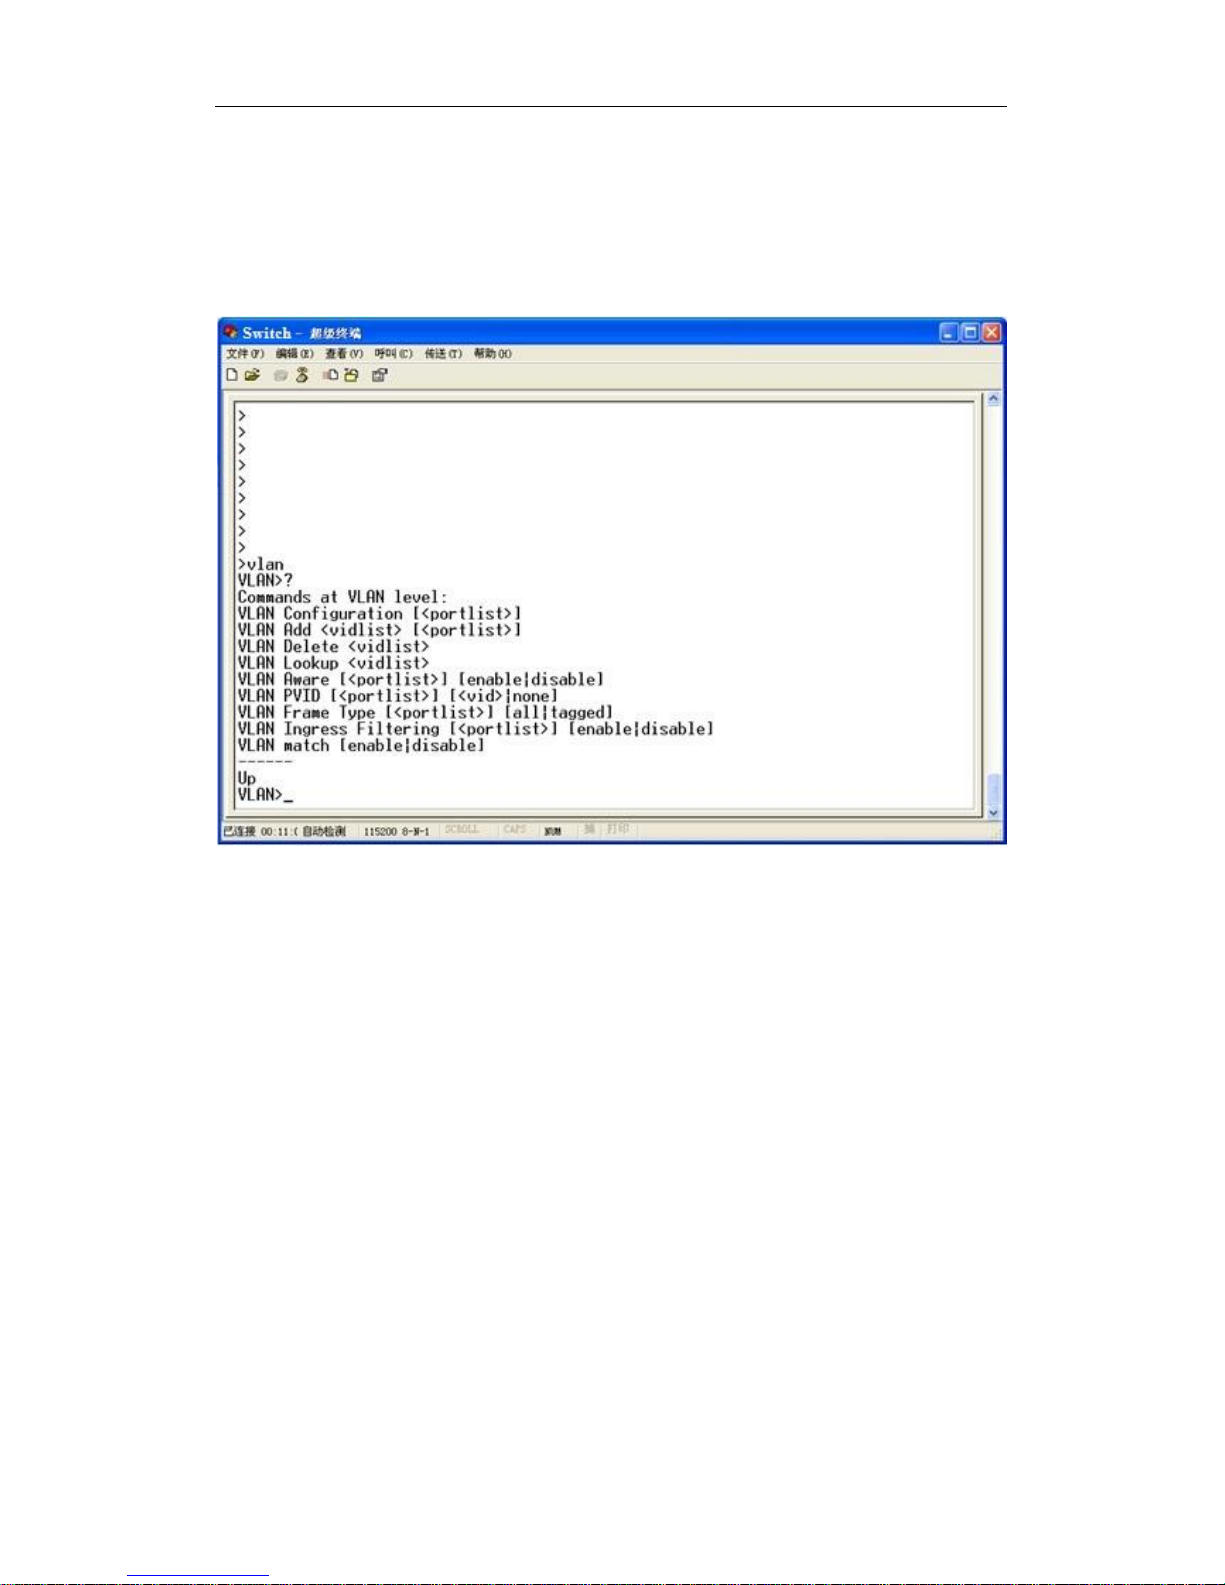
Chapter 5 VLAN Configuration
Input “vlan” command to enter into vlan configuration model, as below picture showed.
Picture 3.1.5 VLAN configuration
1. VLAN configuration query
Command: Configuration[<portlist>]
[<portlist>]-port number list, 1,2,4-5 for option
Description:query VLAN configuration of specified ports,default configuration is for all
ports.
2. Add VLAN
Command: Add <vidlist> [<portlist>]
<vidlist>
[<portlist>]-port number list, 1,2,4-5 for option
Description:query VLAN configuration of specified ports,default configuration is for all
ports.
3. Delete VLAN
Command: Delete <vidlist>
<vidlist>-VLAN list, like 1,3,5-6
Description:delete one group of VLAN, the related PVID will also be deleted
4. Look up VLAN
Command: Lookup <vidlist>
<vidlist>-VLAN list, single VLAN or a group of VLAN ID(like 1,3,5-6)
Description: look up VLAN related port information
Page 40
User’s Guide
Page 40 of 54
5. TAG configuration
Command: Aware [enable|disable]
[<portlist>] -port number list, like1,2,4-5
Enable-tag the exgress packets
Disable-untag the exgress packets
Description: configure the tag function
6. Port PVID
Command: PVID [<portlist>] [<vid>|none]
[<portlist>] -port number list, like1,2,4-5
[<vid>|none]-VLAN ID, if configured as none, refers to the default VLAN is adopted
Description: configure the default VLAN ID of single port
7. Configure the type of receiving frame
Command: VLAN Frame Type [<portlist>] [all|tagged]
[<portlist>] -port number list, default as all ports
All refers to receive all types of frames, including untagged frames,tagged frames and
tagged
frames with VLAN ID configured as 0.
Tagged refers to receive tagged frames only, and the tagged VLAN ID won’t be 0
8. VLAN ingress filtering
Command: Ingress Filtering [<portlist>] [enable|disable]
[<portlist>]-port number list, like1,2,4-5
Enable-refers to abandon the unmatched VLAN
Disable-refers to accept the unmatched VLAN
Description: configure how to deal with illegal VLAN, default as accepting unmatched
VLAN.
9. Configure match VLAN
Command: VLAN match [enable|disable]
Enable-refers to matched VLAN
Disable-refers to unmatched VLAN
Description: configure to match VLAN information when looking up MAC address table
Chapter 6 ARP Configuration
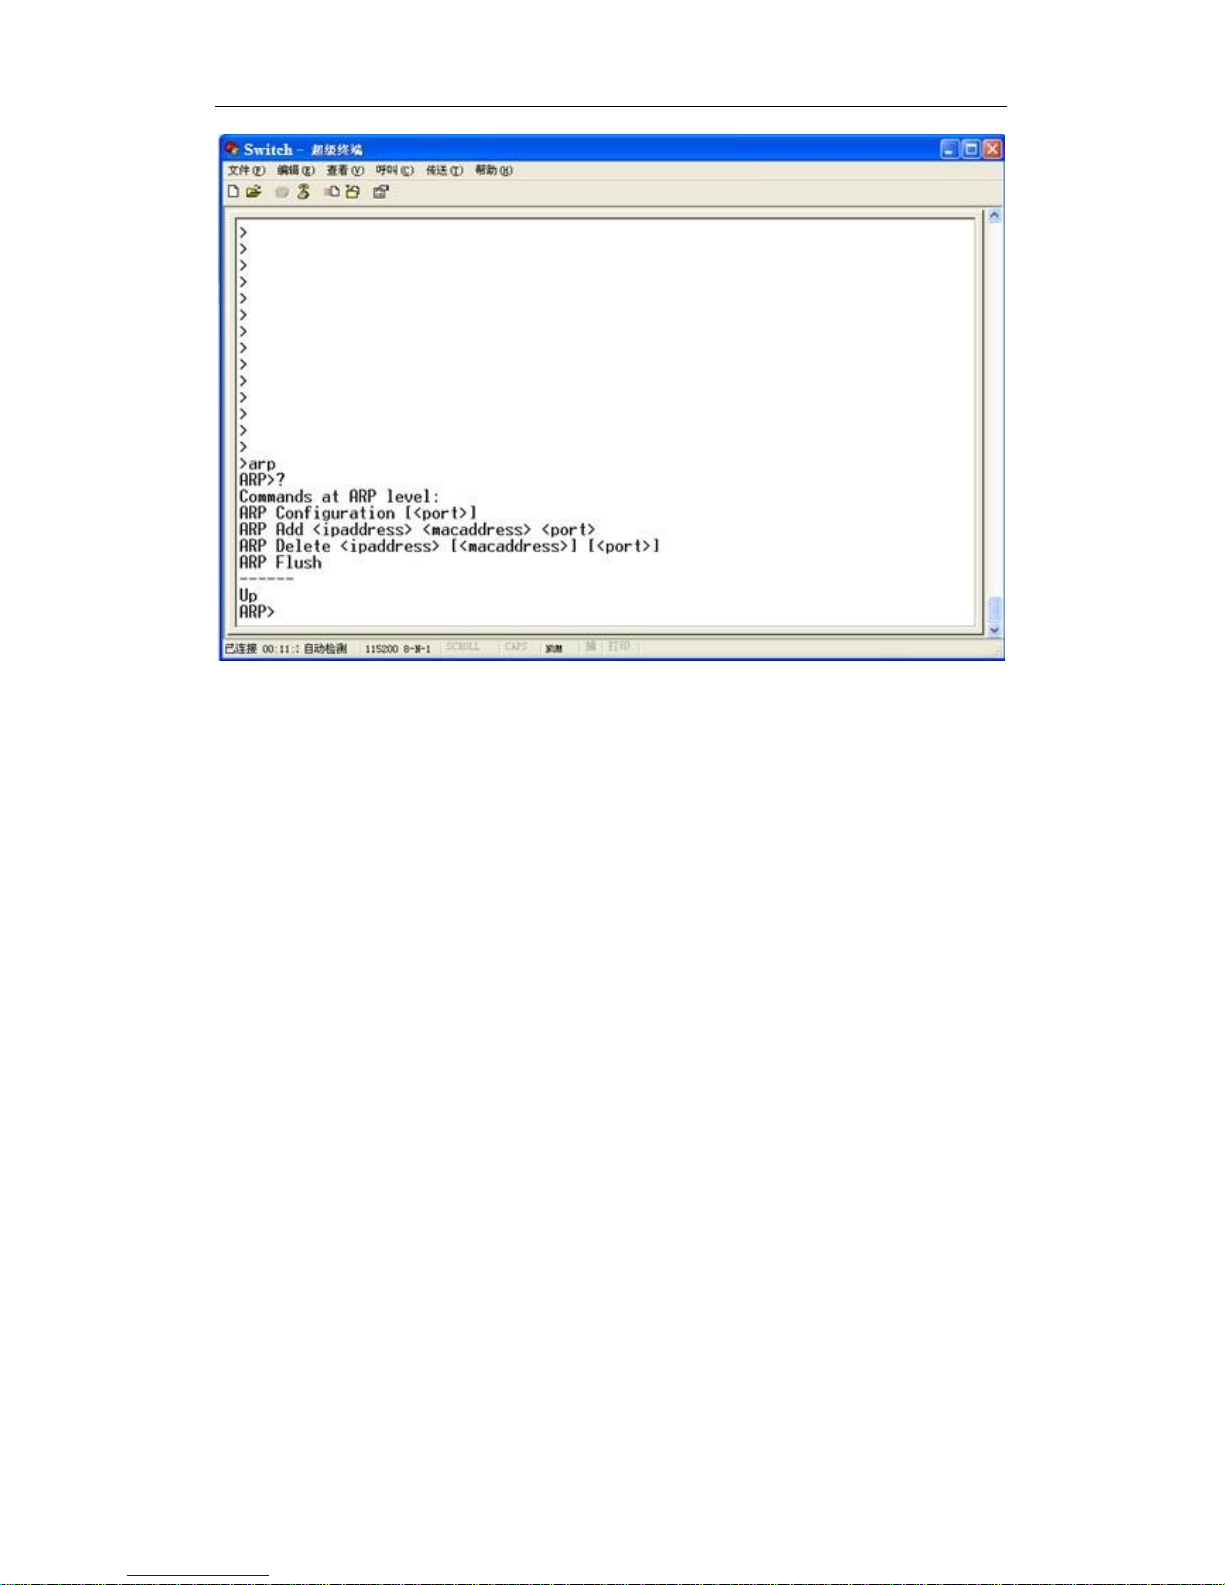
Input “arp” command to enter into ARP configuration mode.
Page 41
User’s Guide
Page 41 of 54
Picture 3.1.6 ARP configuration
1. Look up ARP configuration
Command:Configuration [<port>]
<port>-port number list, like 1,2,4-5
Description:look up the ARP configuration of specified ports, default as all ports
2. Add ARP
Command:Add <ipaddress> <macaddress> <port>
<ipaddress>-IP address
<macaddress>-MAC address
<port>-port number
Description:add ARP under specified ports
3. Delete ARP
Command:Delete <ipaddress> [<macaddress>] [<port>]
<ipaddress>-IP address
<macaddress>-MAC address
<port>-port number
Description:delete ARP under specified ports
4. Clear all ARP
Command:Flush
Description: clear all ARP configuration
Chapter 7 Link Aggregation Configuration
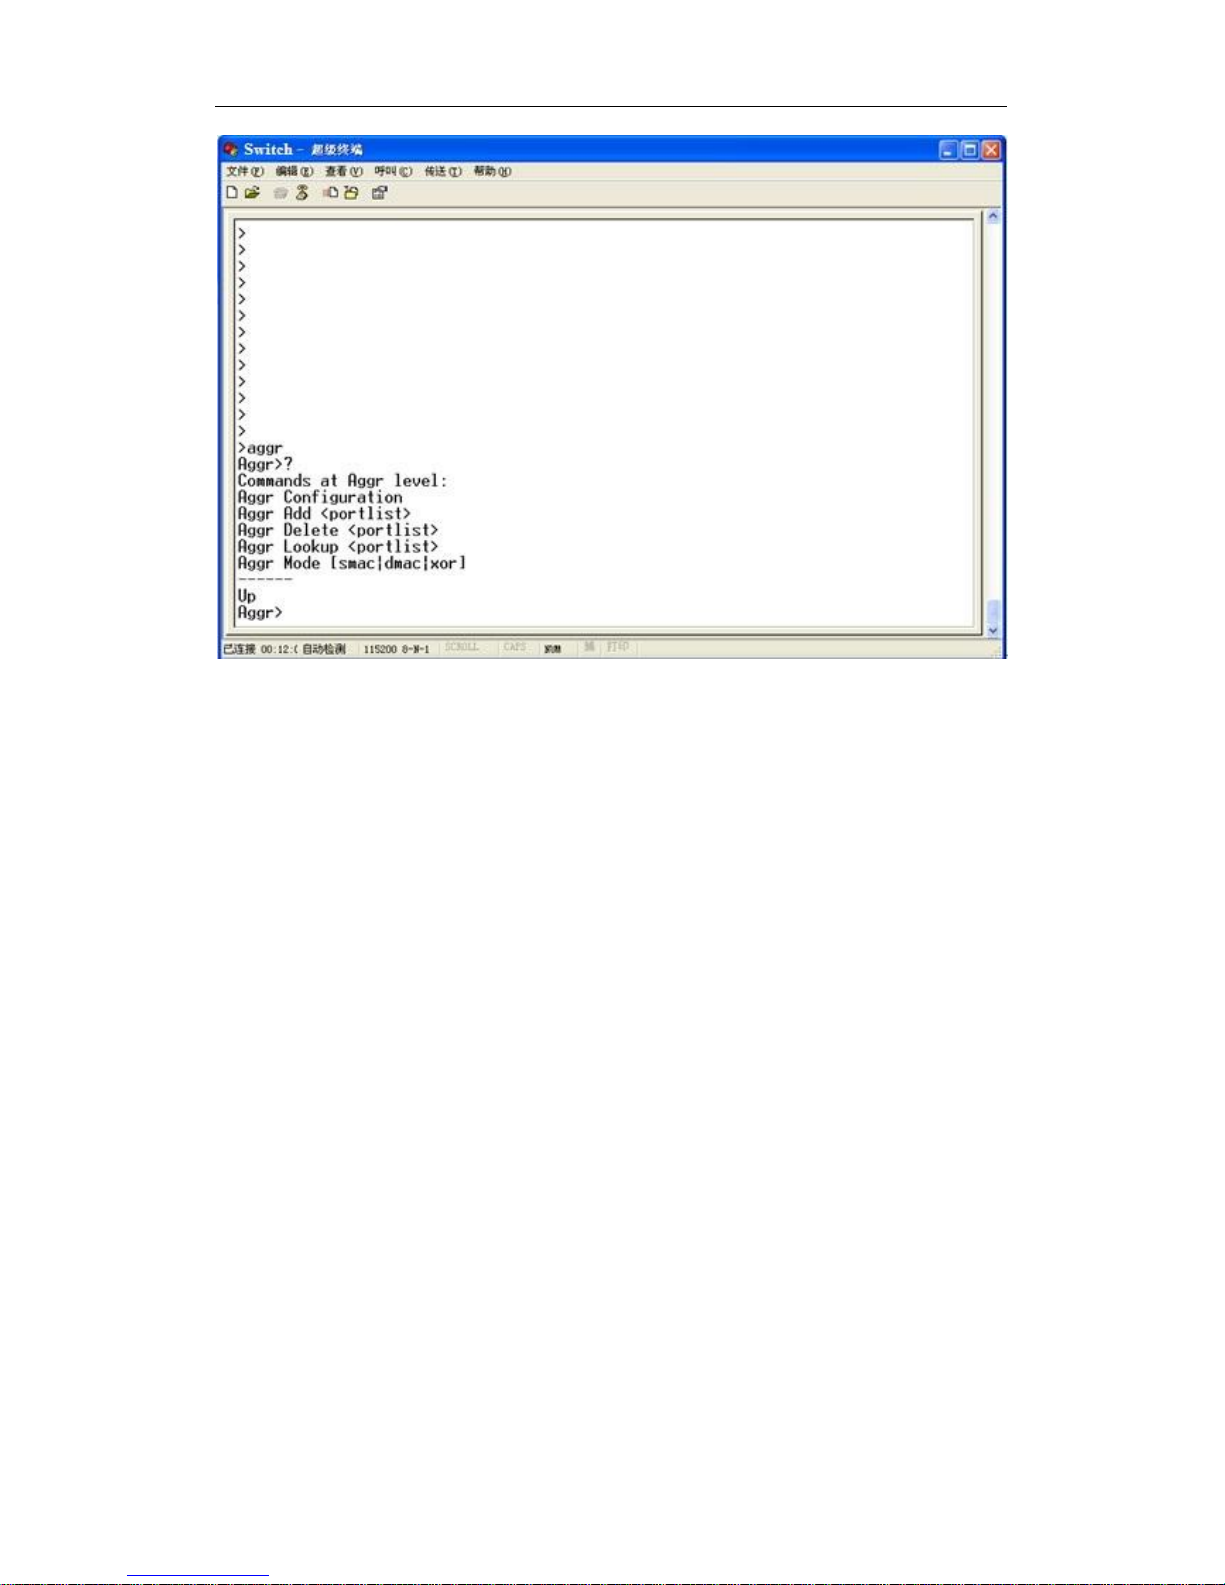
Input “aggr” command to enter into link aggregation configuration mode.
Page 42
User’s Guide
Page 42 of 54
Picture 3.1.7 Link Aggregation Configuration
1. Look up aggregation configuration
Command: Configuration
Description:look up link aggregation configuration information
2. Add port aggregation group
Command: Add <portlist>
[<portlist>] -port number list, like 1,2,4-5
Description:create a aggregator group and configure the port list
3. Delete port aggregation group
Command: Delete <portlist>
[<portlist>] -port number list, like 1,2,4-5
Description:delete a aggregator group
4. Look up port aggregation group
Command: Lookup <portlist>
[<portlist>] -port number list, like 1,2,4-5
Description: look up the aggregator group of specified ports
5. Configure the load share of link aggregation
Command: Aggr Mode [smac|dmac|xor]
Smac-packet based source MAC address load share
Dmac-packet based destination MAC address load share
Xor-packet based source and destination MAC address load share
Description: load share is a overall method.
Chapter 8 LACP Configuration
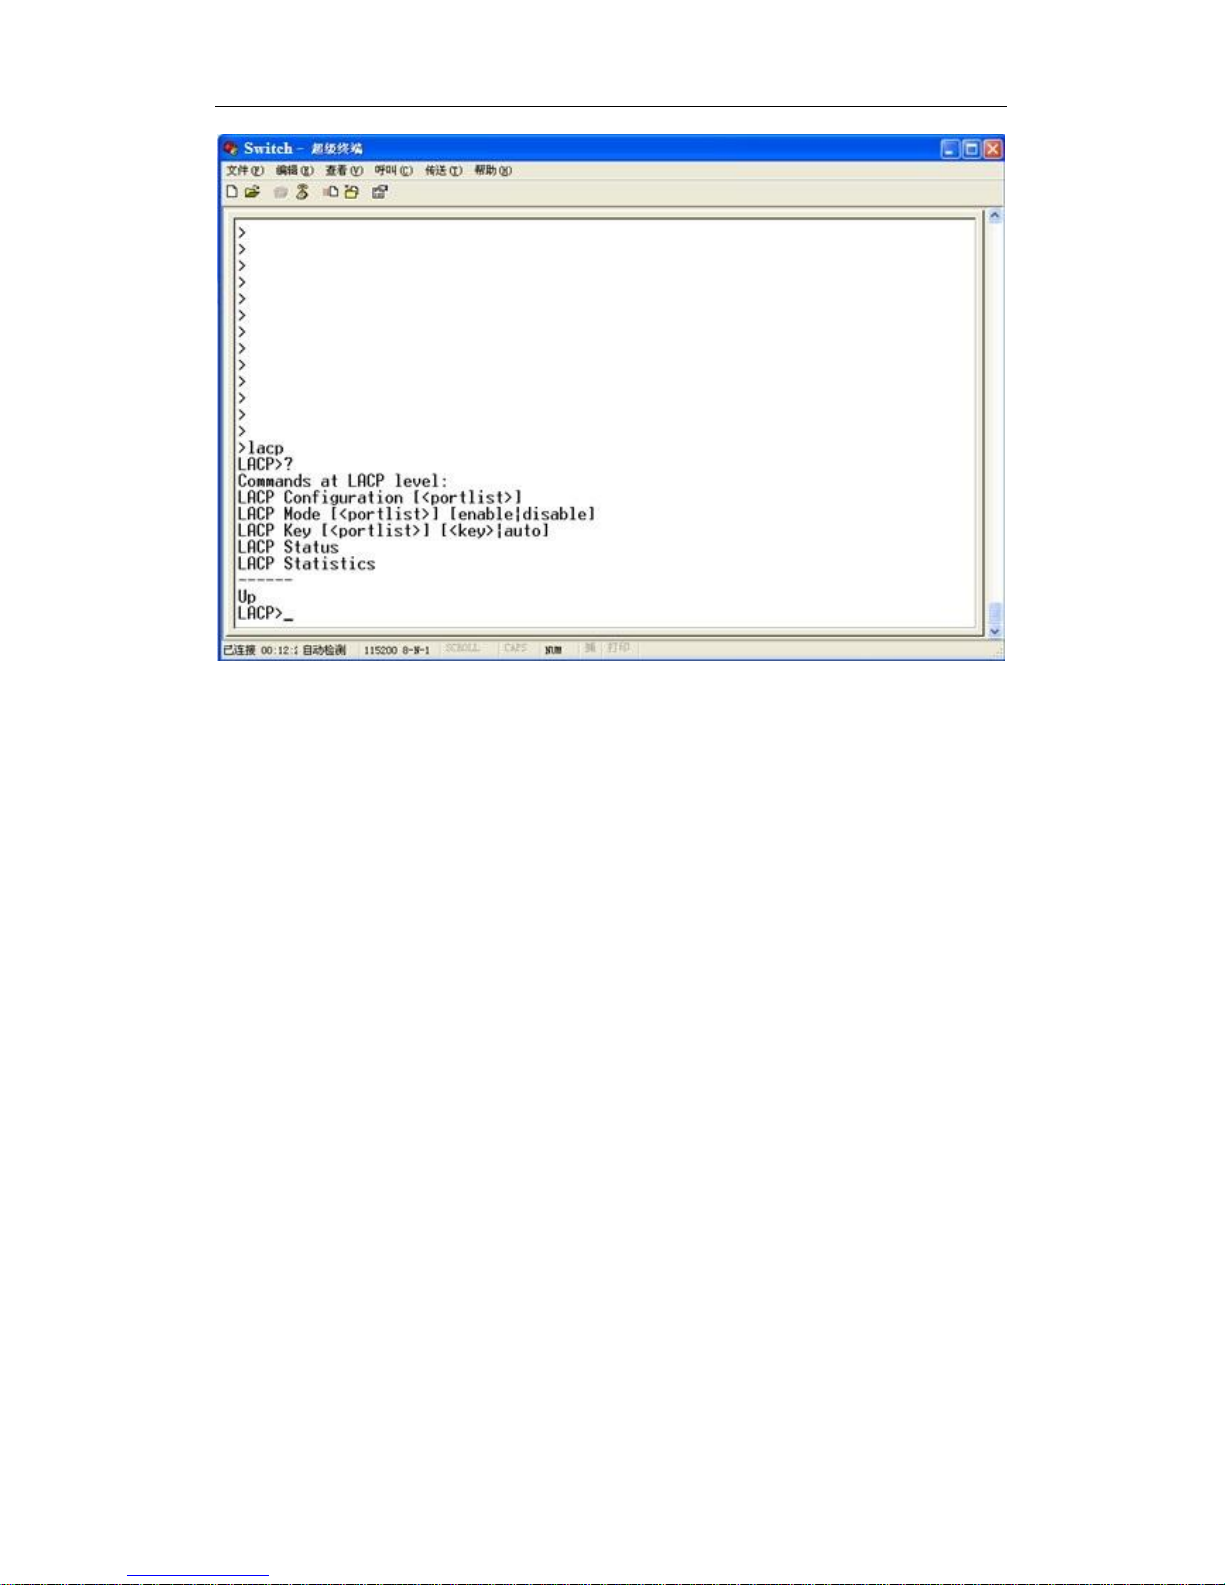
Input “lac” command to enter into LACP configuration mode.
Page 43
User’s Guide
Page 43 of 54
Picture 3.1.8 LACP configuration
1. Display LACP configuration information
Command:LACP Configuration [<portlist>]
[<portlist>]-port number list, like 1,2,4-5
Description:display the LACP config information of specified port
2. Configure LACP protocol of specified port
Command:LACP Mode [<portlist>] [enable|disable]
[<portlist>]-port number list, like 1,2,4-5
Description: configure the state of LACP protocol
3. Configure Key number of specified port
Command:LACP Key [<portlist>] [<key>|auto]
[<portlist>]-port number list, like 1,2,4-5, default as all ports
[<key>]-key range is 1-255;[Auto] refers to auto-negotiation Key number.
Description: configure the Key number
4. Look up the state of LACP groups and ports
Command:LACP status
Description: look up the following information: state of LACP groups and ports, current
group number ID,current port ID,the MAC address and port ID of end devices.
5. Look up LACP statistics
Command:LACP Statistics
Description:Look up the LACP protocol statistics
Chapter 9 RSTP Configuration
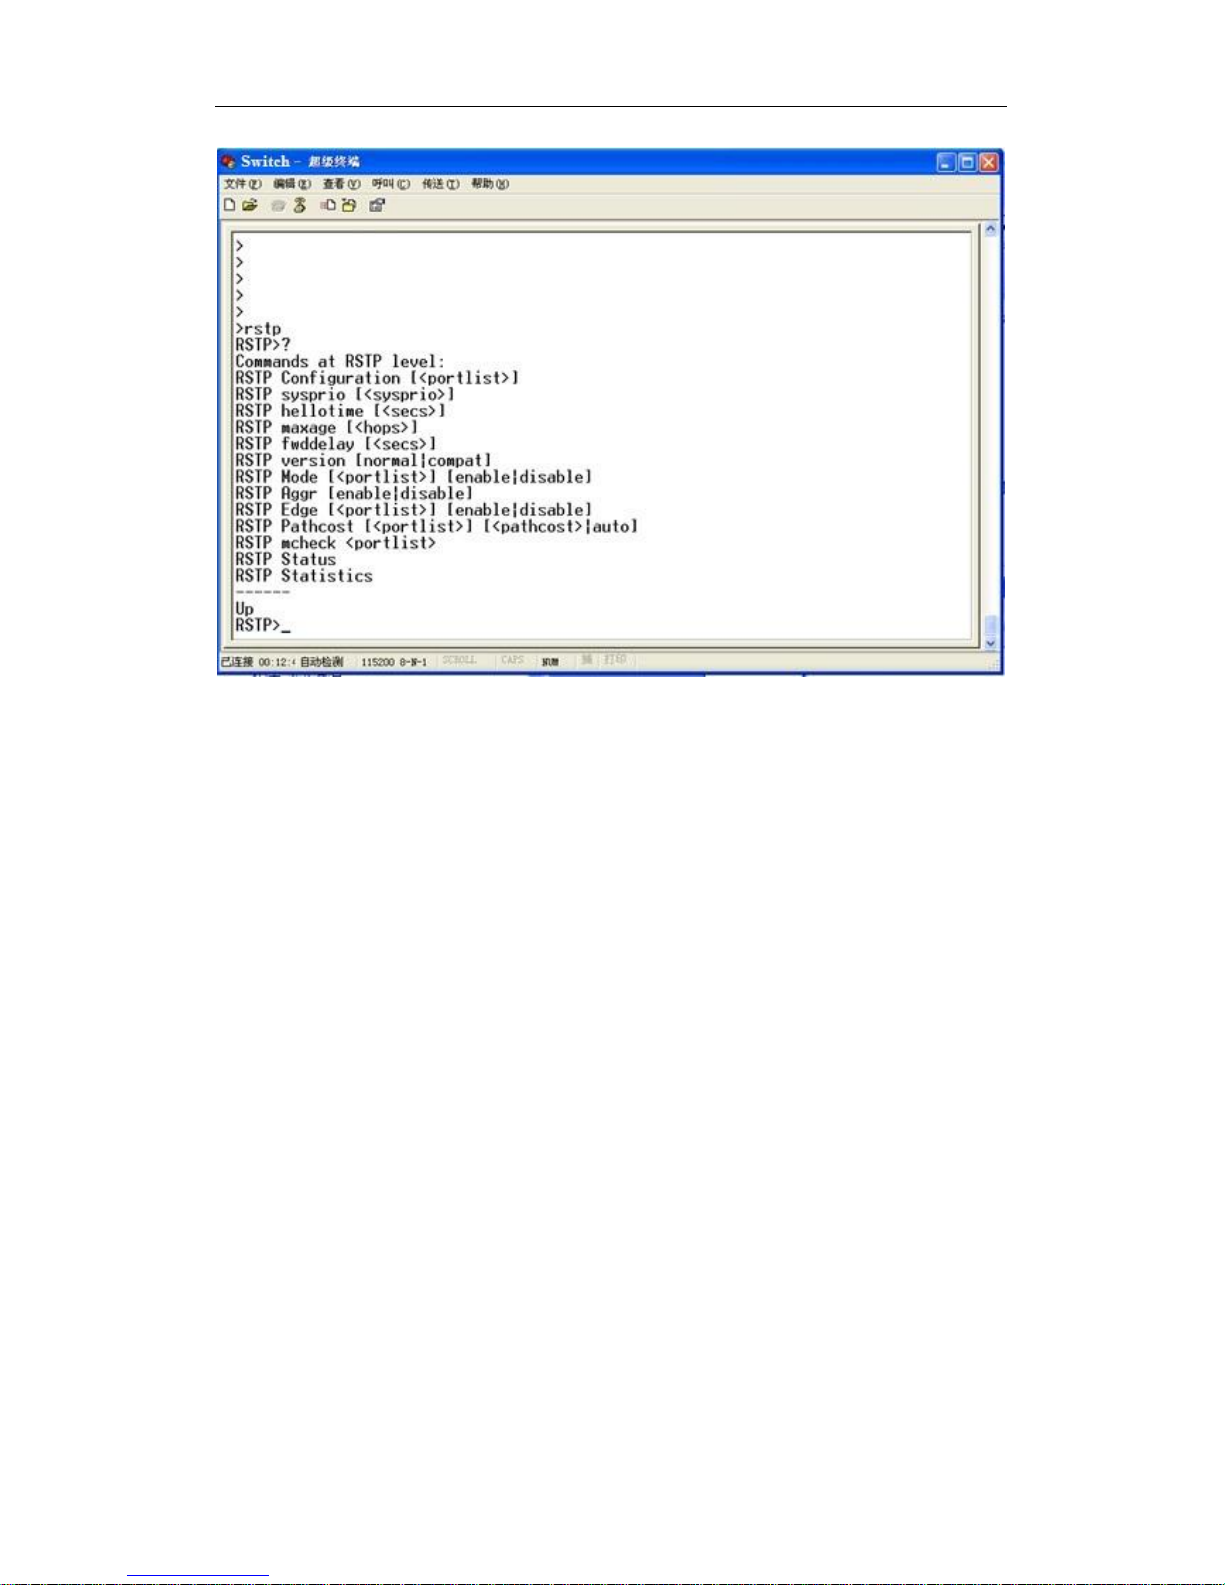
Input “rstp” command to enter into RSTP configuration mode.
Page 44
User’s Guide
Page 44 of 54
1. Display the current RSTP configuration
Command:RSTP Configuration [<portlist>]
[<portlist>]-port number list, like 1,2,4-5
Description:display the RSTP config information
2. Modify the priority class of current switch
Command:RSTP sysprio [<sysprio>]
[<sysprio>]-priority list,0-61440
Description: modify and look up the current RSTP priority class, default as 32768.
3. Modify the hello time of switch
Command:RSTP hello time [<secs>]
[<secs>]-time list
Description:the hello time is among1-10s, default as 2s.
4. Modify the maximum aging time of switch
Command:RSTP maxage[<hops>]
[<hops>]-aging time,among 6-40, default as 20.
Description:modify and look up the maximum aging time of RSTP
5. Modify the delay time of RSTP forwarding
Command:RSTP fwddelay [<secs>]
[<secs>]-time list, among 4-30, default as 15
Description:modify and look up the delay time of RSTP
6. Modify the STP version
Command:RSTP version [normal | compat]
Normal-under this normal version, the switch can recognize both STP and RSTP BPDU
Compat-compatible version, only support STP format BPDU
Description:to modify and look up current STP version, default as Normal.
7. Modify the STP state
Page 45
User’s Guide
Page 45 of 54
Command:RSTP Mode [<portlist>] [enable | disable]
[<portlist >]-port list,like 1,2,4-5, default as all ports
Enable-switch on RSTP
Disable-Switch off RSTP
Description:modify the STP states of single port
8. Modify the RSTP state in current link aggregation
Command:RSTP aggr [enable | disable]
Enable-switch on RSTP in the link aggregation
Disable-Switch off RSTP in the link aggregation
Description:modify the RSTP states in the link aggregation
9. Configure the edge ports of Spanning Tree Protocol
Command:RSTP edge [<portlist>] [enable | disable]
[<portlist >]-port list,like 1,2,4-5
Enable- configure the port as RSTP edge port
Disable-cancel the port as RSTP edge port
Description:configure the edge ports of RSTP, defaulted as all ports
10. Modify the pathcost of STP ports
Command:RSTP pathcost [<portlist>] [<pathcost> | auto]
[<portlist >]-port list,like 1,2,4-5,defaulted as all ports
<pathcost>-among 1-200000000)
Auto-automatic calculate past cost
Description:Modify the pathcost of RSTP, smaller number means upper priority class
11. Remove ports to RSTP mode
Command:RSTP mcheck <portlist>
<portlist>-port list,like 1,2,4-5
Description:remove specified port to RSTP mode
12. RSTP status
Command: RSTP status
Description:look up the RSTP system information and port information
13. RSTP statistics
Command: RSTP Statistics
Description:Statistic the RSTP port information
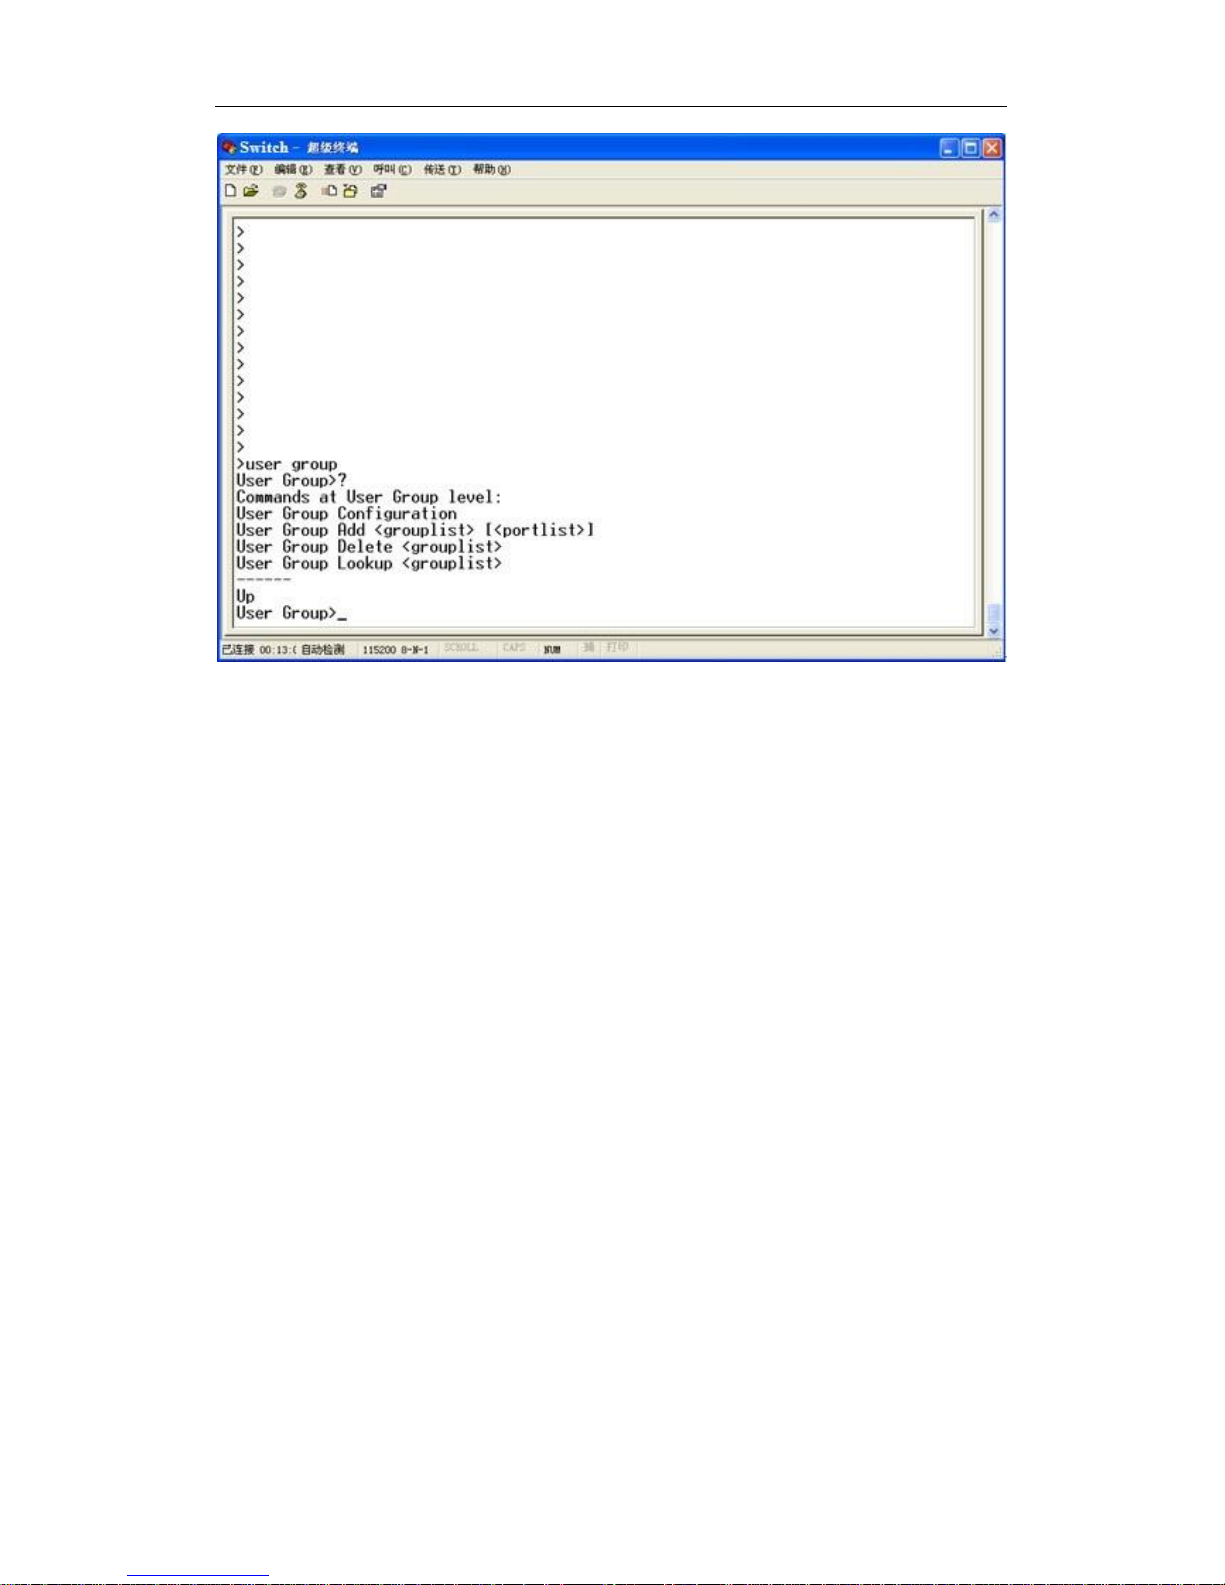
Chapter 10 User Group Configuration
Input “User Group” command to enter into User Group configuration mode.
Page 46
User’s Guide
Page 46 of 54
Picture 3.1.10 User Group Configuration
1. Display the current user group configuration
Command:User Group Configuration
Description:display the current user group configuration, include user group list and user
ID list.
2. Create user group or add new port to an user group
Command:User Group Add <grouplist> [<portlist>]
<grouplist> -the group list range from 1~24
<portlist>-Port list, default as all ports.
Description: when a specified group list is not existed, please create a new group list and
add specified ports to the list;when the user group is existed, please add the specified
ports to list.
3. Delete specified user group
Command:User Group Delete <grouplist>
<grouplist>-group list, like 1,2,4-5
Description: Delete the selected user group.
4. Look up specified user group
Command:User Group Lookup <grouplist>
<grouplist>-group list, range from 1~24, like 1,2,4-5
Description: Look up specified user group,display the port ID list of user group
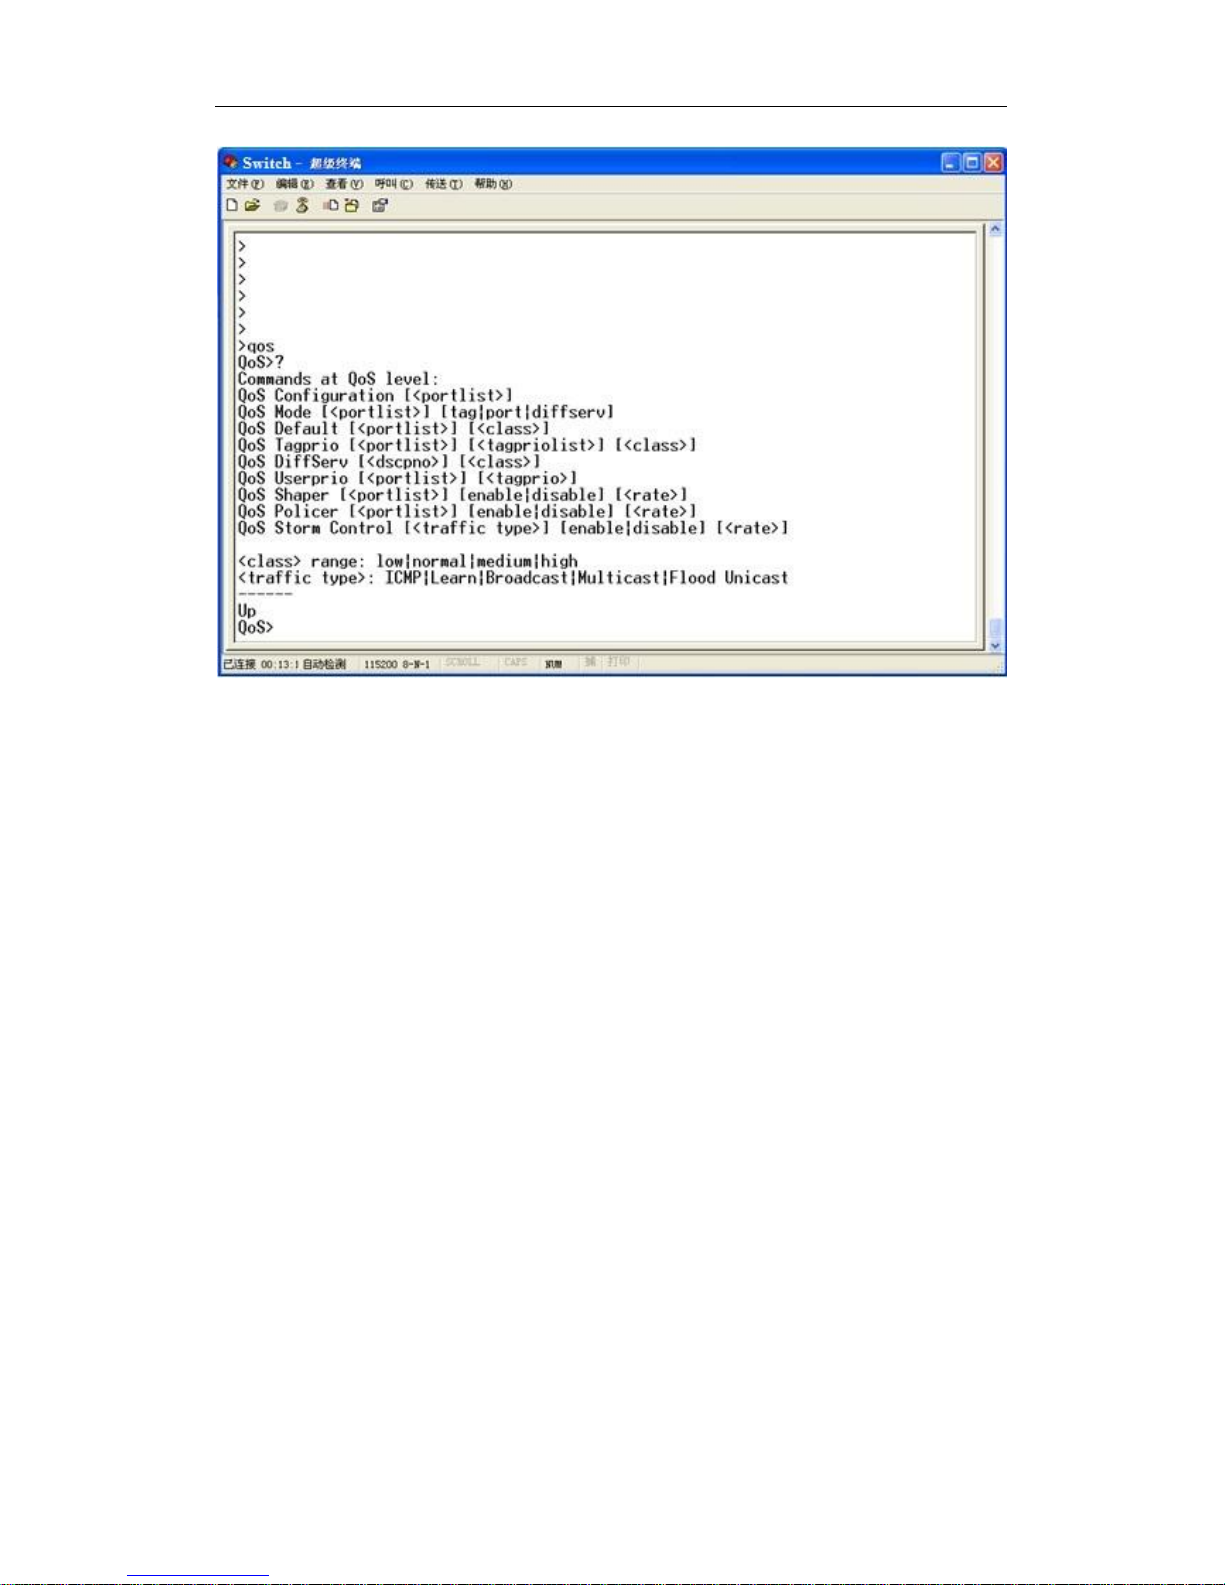
Chapter 11 QoS Configuration
Input “qos” command to enter into QoS configuration mode.
Page 47
User’s Guide
Page 47 of 54
Picture 3.1.11 QoS configuration
1. Look up QoS configuration
Command:Configuration [<portlist>]
[<portlist>]-port list, like 1,2,4-5
Description: Look up QoS configuration information
2. QoS working modes
Command: Mode [<portlist>] [tag|port|diffserv]
[<portlist>]-port list, like 1,2,4-5
Tag-support 802.1Q
Port-support port-based QoS
Diffserv-support differentiated services
Description: configure the QoS type of specified port
3. Port priority class
Command:Default [<portlist>] [<class>]
[<portlist>]-port list,like 1,2,4-5
[<class>]-priority class, include:low,normal,medium,high
Description: configure the priority class of specified ports, low is the lowest priority.
4. 802.1Q priority conversion
Command:Tagprio [<portlist>] [<tagpriolist>] [<class>]
[<portlist>]-port list,like 1,2,4-5
[<tagpriolist>] -the priority class of TAG range from 0 to 7
[<class>]-priority class, include:low,normal,medium,high
Description:configure how to convert the 802.1Q priority class to local processing priority
5. Differentiated services conversion
Command:DiffServ [<dscpno>] [<class>]
[<dscpno>] -the differentiated service rane of IP packets is 1~63
Page 48
User’s Guide
Page 48 of 54
[<class>]-priority class, include:low,normal,medium,high
Description:configure how to convert the DiffServ priority class to local processing priority
6. Priority for 802.1 Q output
Command:Userprio [<portlist>] [<tagprio>]
[<portlist>]-port list,like 1,2,4-5
[<tagprio>] -the priority class of tagged packet outputing
7. Flow control for ingress packets
Command:Shaper [<portlist>] [enable|disable] [<rate>]
[<portlist>]-port list,like 1,2,4-5
[enable|disable]-enable or disable the flow control switch
<rate>-ingress limit, range from0~3968K
Description:configure the maximum ingress limit, the unit is bits/s
Example:Shaper 1-2 enable 128K
8. Flow control for egress packets
Command:Policer [<portlist>] [enable|disable] [<rate>]
[<portlist>]-port list,like 1,2,4-5
[enable|disable]-enable or disable the flow control switch
<rate>-egress limit, range from0~3968K
Description:configure the maximum egress limit, the unit is bits/s
Example:Policer 1-2 enable 128K
9. Storm control limit
Command:Storm Control [<traffic type>] [enable|disable] [<rate>]
[<traffic type>] -storm control type:include:ICMP|Learn|Broadcast|Multicast|Flood Unicast
[enable|disable]-enable or disable the storm control switch
<rate>-storm control value, unit is pps.
Description:configure the flow control value of specified broadcast storm.
Chapter 12 Port Mirror Configuration
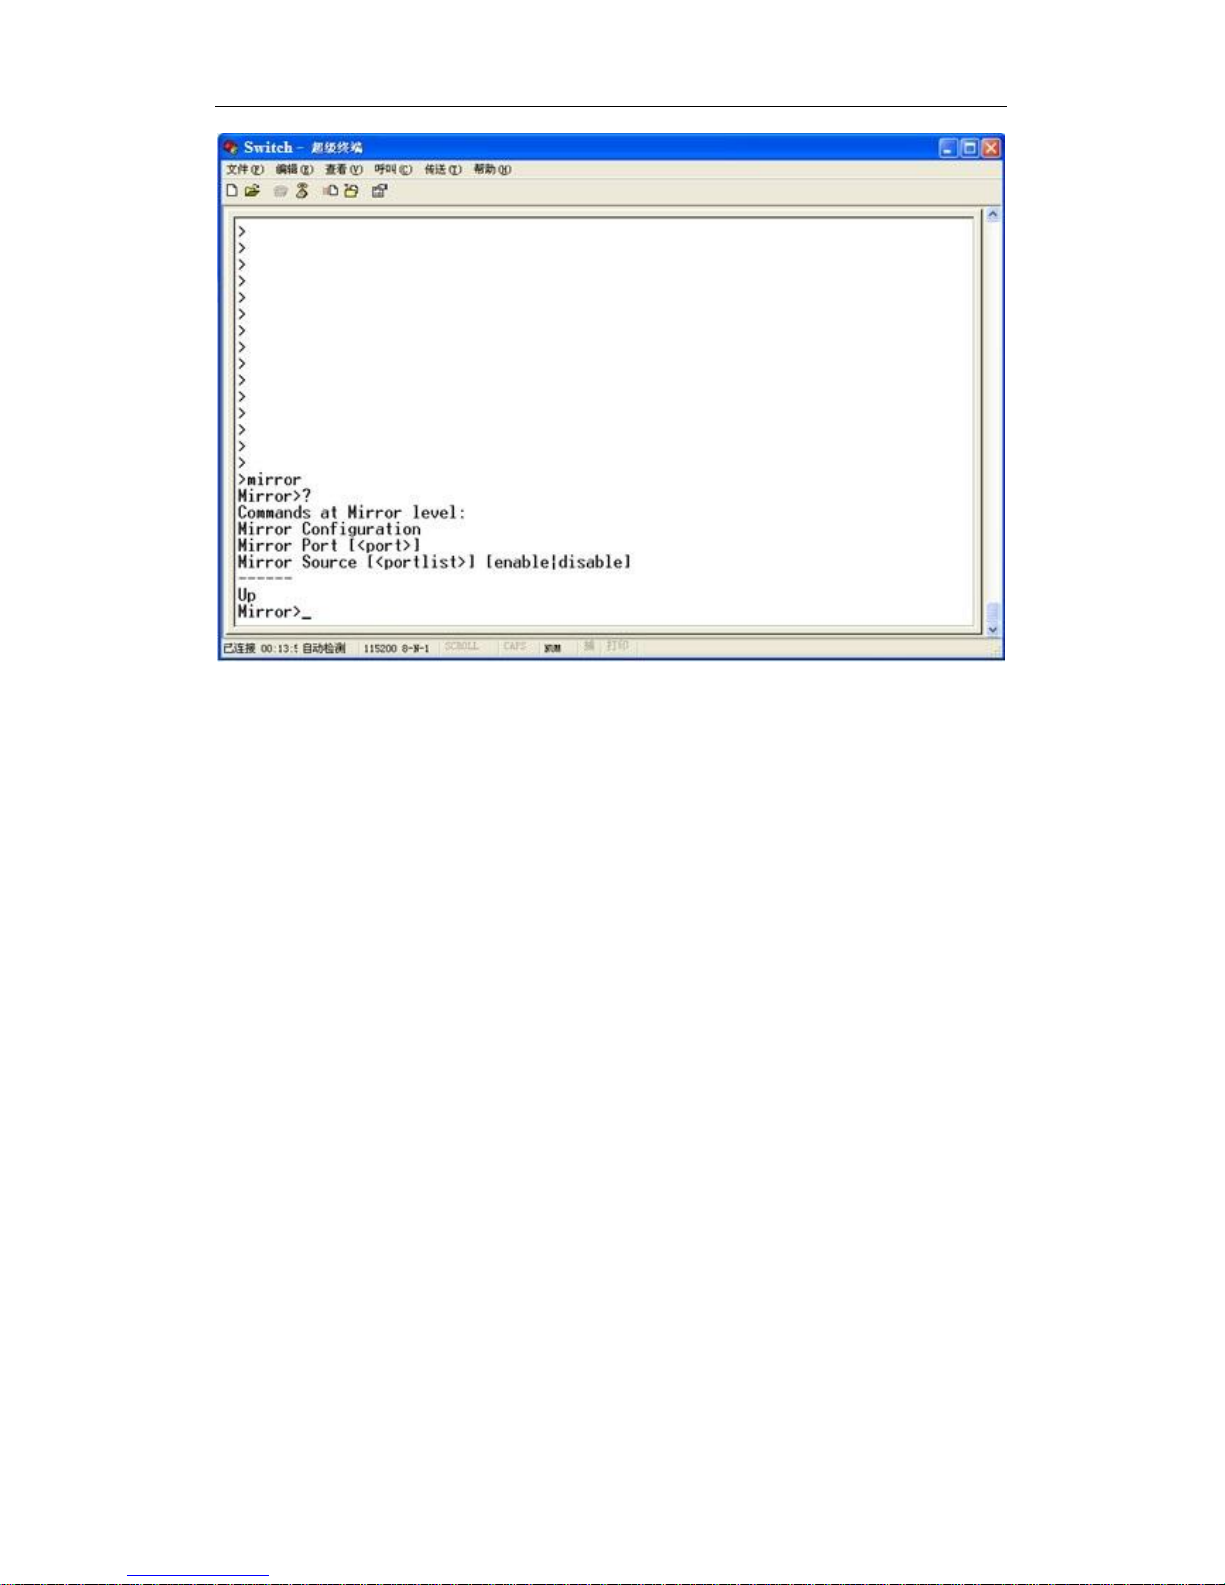
Input “mirror” command to enter into port mirror configuration mode.
Page 49
User’s Guide
Page 49 of 54
Picture 3.1.12 Port Mirroring Configuration
1. Look up the port mirror configuration
Command:configuration
Description:look up the port mirror configuration
2. Mirror destination port
Command:Port [<port>]
[<port>]-the destination port of mirroring
Description:configure the destination port of mirroring
3. Mirror source port
Command:Source [<portlist>] [enable|disable]
[<portlist>]-port list,like 1,2,4-5
Enable-allow to input mirror
Disable-not allow to input mirror
Description:configure the source por of mirroring
Chapter 13 IP Address Configuration
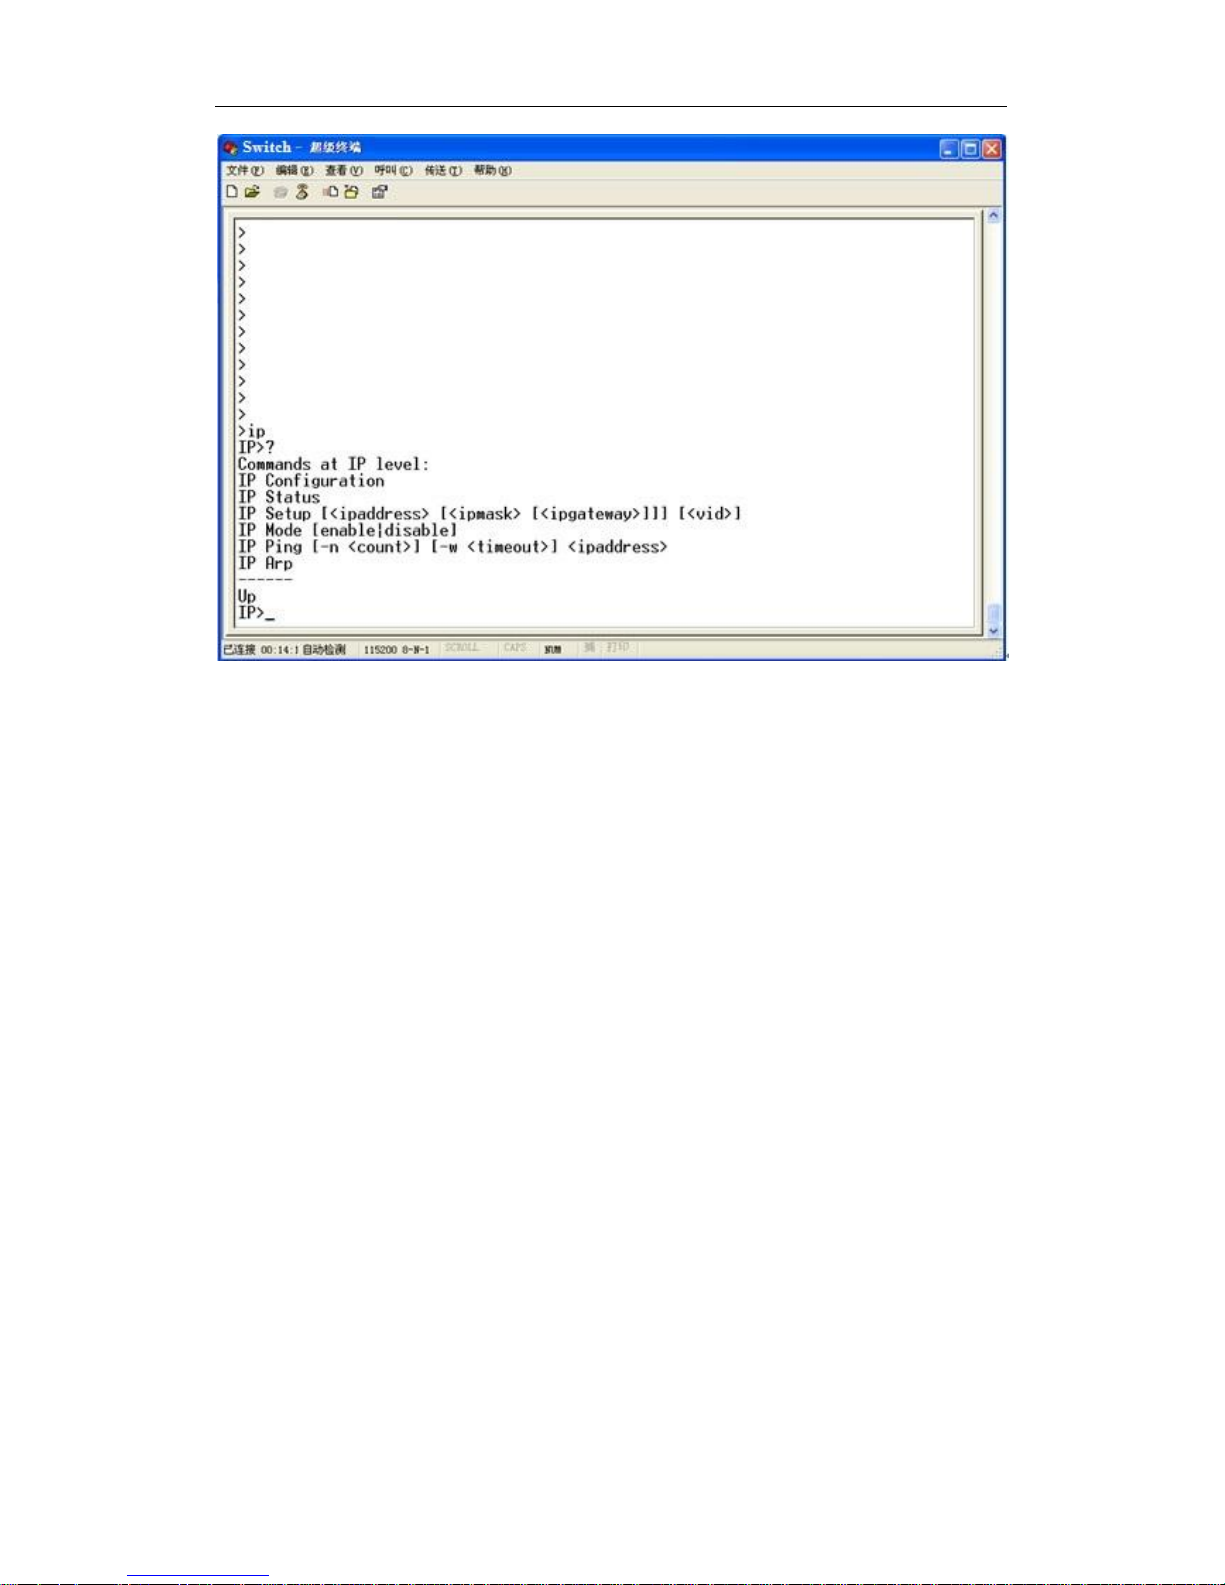
Input “ip” command to enter into IP address configuration mode.
Page 50
User’s Guide
Page 50 of 54
Picture 3.1.1.13 IP address configuration
1. Look up IP address configuration
Command:configuration
Description:look up the IP address configuration
2. Management IP address
Command:Setup [<ipaddress> [<ipmask> [<ipgateway>] [<vid>]
<ipaddress> -IP address
<ipmask> -IP net mask
<ipgateway> -IP gateway
<vid> -management VLAN ID, default as 1
Description: configure the management IP address
3. Enable/Disable switch of IP visit
Command:Mode [enable|disable]
Enable-the switch can be accessed with IP addresses
Disable-the switch can’t be accessed with IP addresses
Description:configure the HTTP visit via IP address, default as supported.
4. Ping function
Command:Ping [-n <count>] [-w <timeout>] <ipaddress>
[-n <count>]-Ping times
[-w <timeout>] -the delay time of PING failure
<ipaddress>-IP address for PING
Description:PING function works when testing the connectivity between switch and other
end devices.
5. ARP address query
Command:Arp
Description:Look up the ARP table created by the switch
Page 51
User’s Guide
Page 51 of 54
Chapter 14 Dot1x Configuration
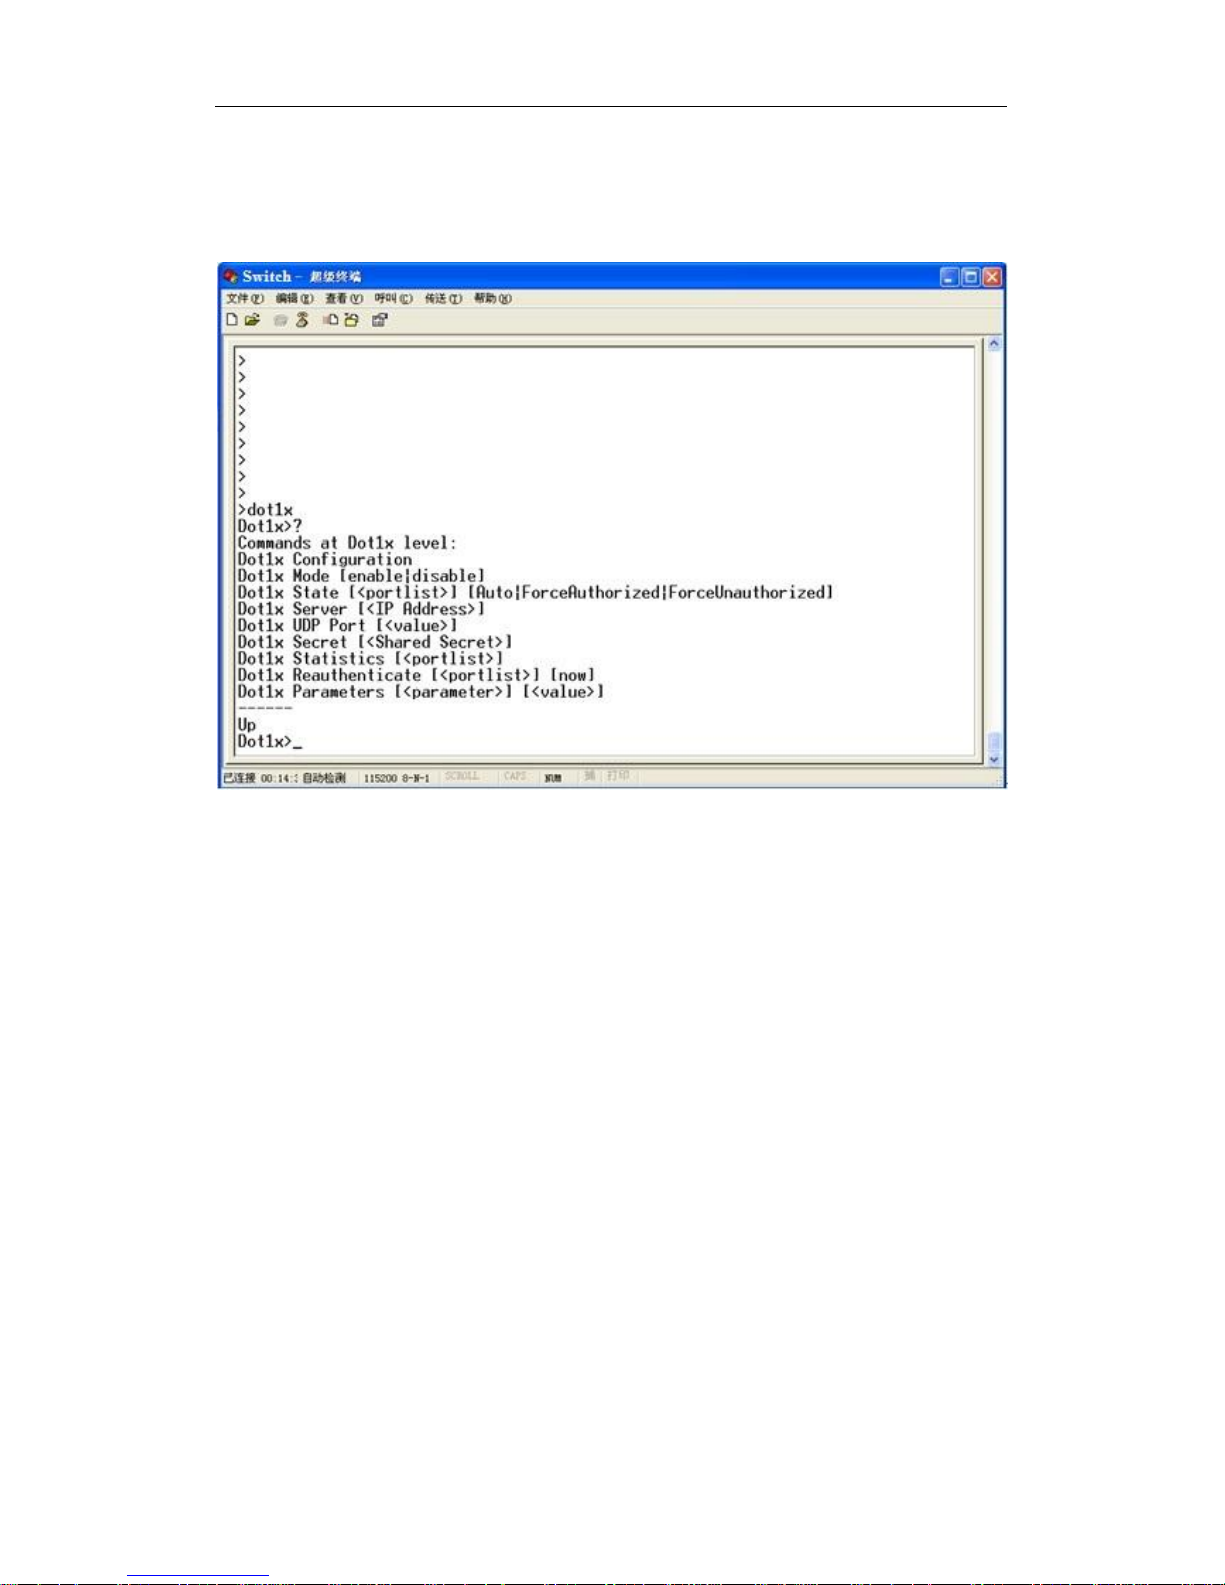
Input “dotlx” command to enter into dot1x configuration mode.
Picture 3.1.14 Dot1x Configuration
1. Look up Dot1x configuration
Command: Dot1x Configuration
Description:Look up Dot1x configuration
2. Configure Dot1x authentication mode
Command:Dot1x Mode [enable|disable]
Enable-Dot1x function works
Disable-Close Dot1x funcion
Description:enable or disable Dot1x function
3. Configure the Dot1x authentication status
Command:Dot1x State [<portlist>] [Auto|ForceAuthorized|ForceUnauthorized]
[<portlist>] -port list,like 1,2,4-5,default as all ports
[Auto] -automatically authentication
[ForceAuthorized] -force authorization
[ForceUnauthorized]-force unauthorization
Description:configure the Dot1x authentication status
4. Configure RADIUS server IP address
Command:Dot1x Server [<IP Address>]
[<IP Address>]-RADIUS server IP address
Description:configure RADIUS server IP address
5. Configure the protocol port ID of RADIUS server
Command:Dot1x UDP Port [<value>]
Page 52
User’s Guide
Page 52 of 54
[<value>] -protocol port ID of RADIUS server
Description:configure the protocol port ID of RADIUS server
6. Configure RADIUS communication public key
Command:Dot1x Secret [<Shared Secret>]
[<Shared Secret>] -RADIUS communication public key
Description:configure RADIUS communication public key
7. Look up the 802.1X statistics information
Command:Dot1x Statistics [<portlist>]
[<portlist>] -port list,like 1,2,4-5,default as all ports
Description:look up the 802.1X statistics information
8. Configure port reauthentication
Command:Dot1x Reauthenticate [<portlist>] [now]
[<portlist>] -port list,like 1,2,4-5,default as all ports
[now]: immediate reauthentication
Description:Configure port reauthentication
9. Dot1x configuration
Command:Dot1x Parameters [<parameter>] [<value>]
[<parameter>] –Reauthentication,Reauth-period,EAP-Timeout configuration
Description:te Reauthentication function is closed in default, Reauth-period is 3600s,
EAP-Timeout is 30s.
Chapter 15 IGMP Configuration
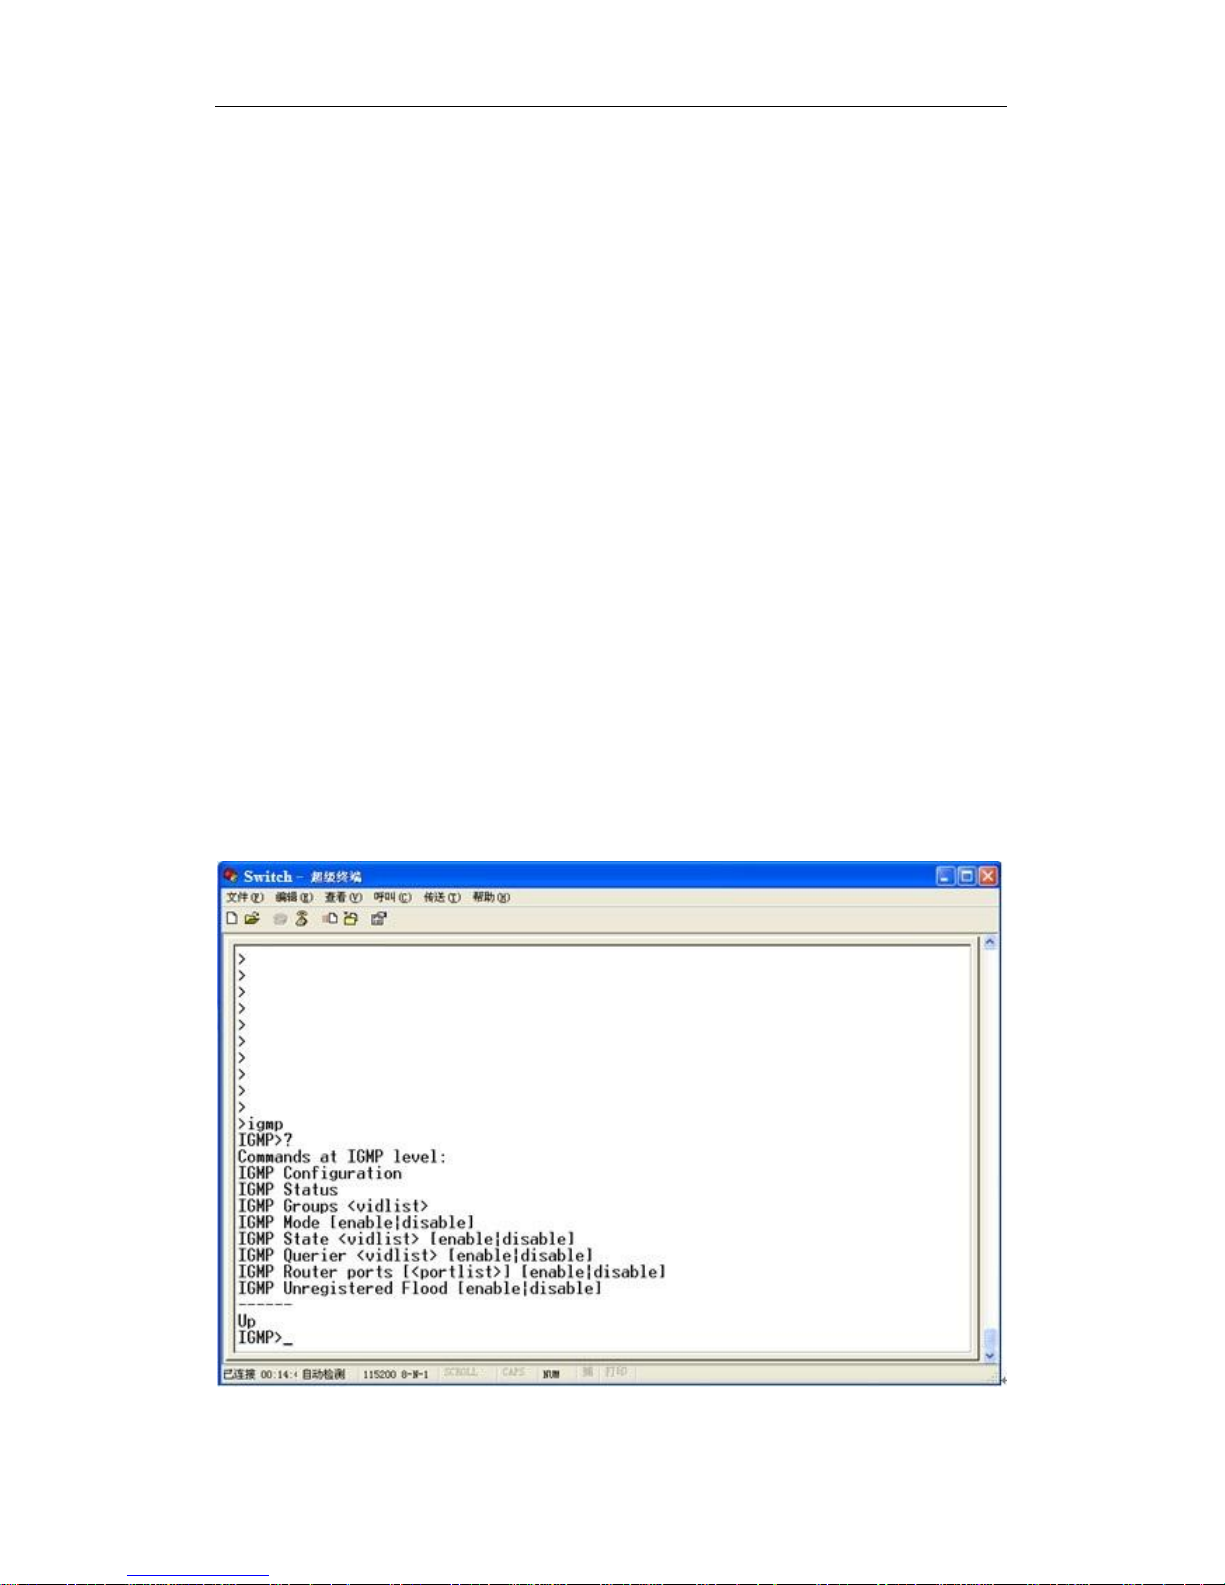
Input “igmp” command to enter into IGMP snooping configuration mode.
Picture 3.1.15 IGMP configuration
1. IGMP snooping configuration
Page 53
User’s Guide
Page 53 of 54
Command:Configuration
Description: look up the IGMP snooping configuration
2. Look up IGMP snooping working status
Command: Status
Description:Look up IGMP snooping working status
3. Multicast VLAN
Command:Groups <vidlist>
<vidlist>-VLAN list
Description: configure the IGMP snooping VLAN groups
4. Enable or disable the IGMP snooping function
Command:Mode [enable|disable]
Description: enable IGMP snooping or not
5. Configure VLAN and enable IGMP snooping funtion
Command:State <vidlist> [enable|disable]
<vidlist>-VLAN list
Enable-open IGMP snooping function
Disable-close IGMP snooping function
Description:configure specified VLAN with IGMP snooping function
6. Look up VLAN configuration
Command:Querier <vidlist> [enable|disable]
<vidlist>-VLAN list
Enable-support IGMP snooping router port negotiation
Disable-not support IGMP snooping router port negotiation
Description:configure specified VLAN with IGMP snooping router port negotiation
7. Router port configuration
Command:Router ports [<portlist>] [enable|disable]
[<portlist>]-port list,like 1,2,4-5
Enable-configure specified port as router port
Disable-disable specified port as router port
Description:static configuration of router port
8. Unregistered multicast processing mode
Command:Unregistered Flood [enable|disable]
Enable- broadcast the Unregistered multicast packets
Disable-abandon the unregistered multicast packets
Description: configure the broadcast of unregistered multicast packets
Page 54
User’s Guide
Page 54 of 54
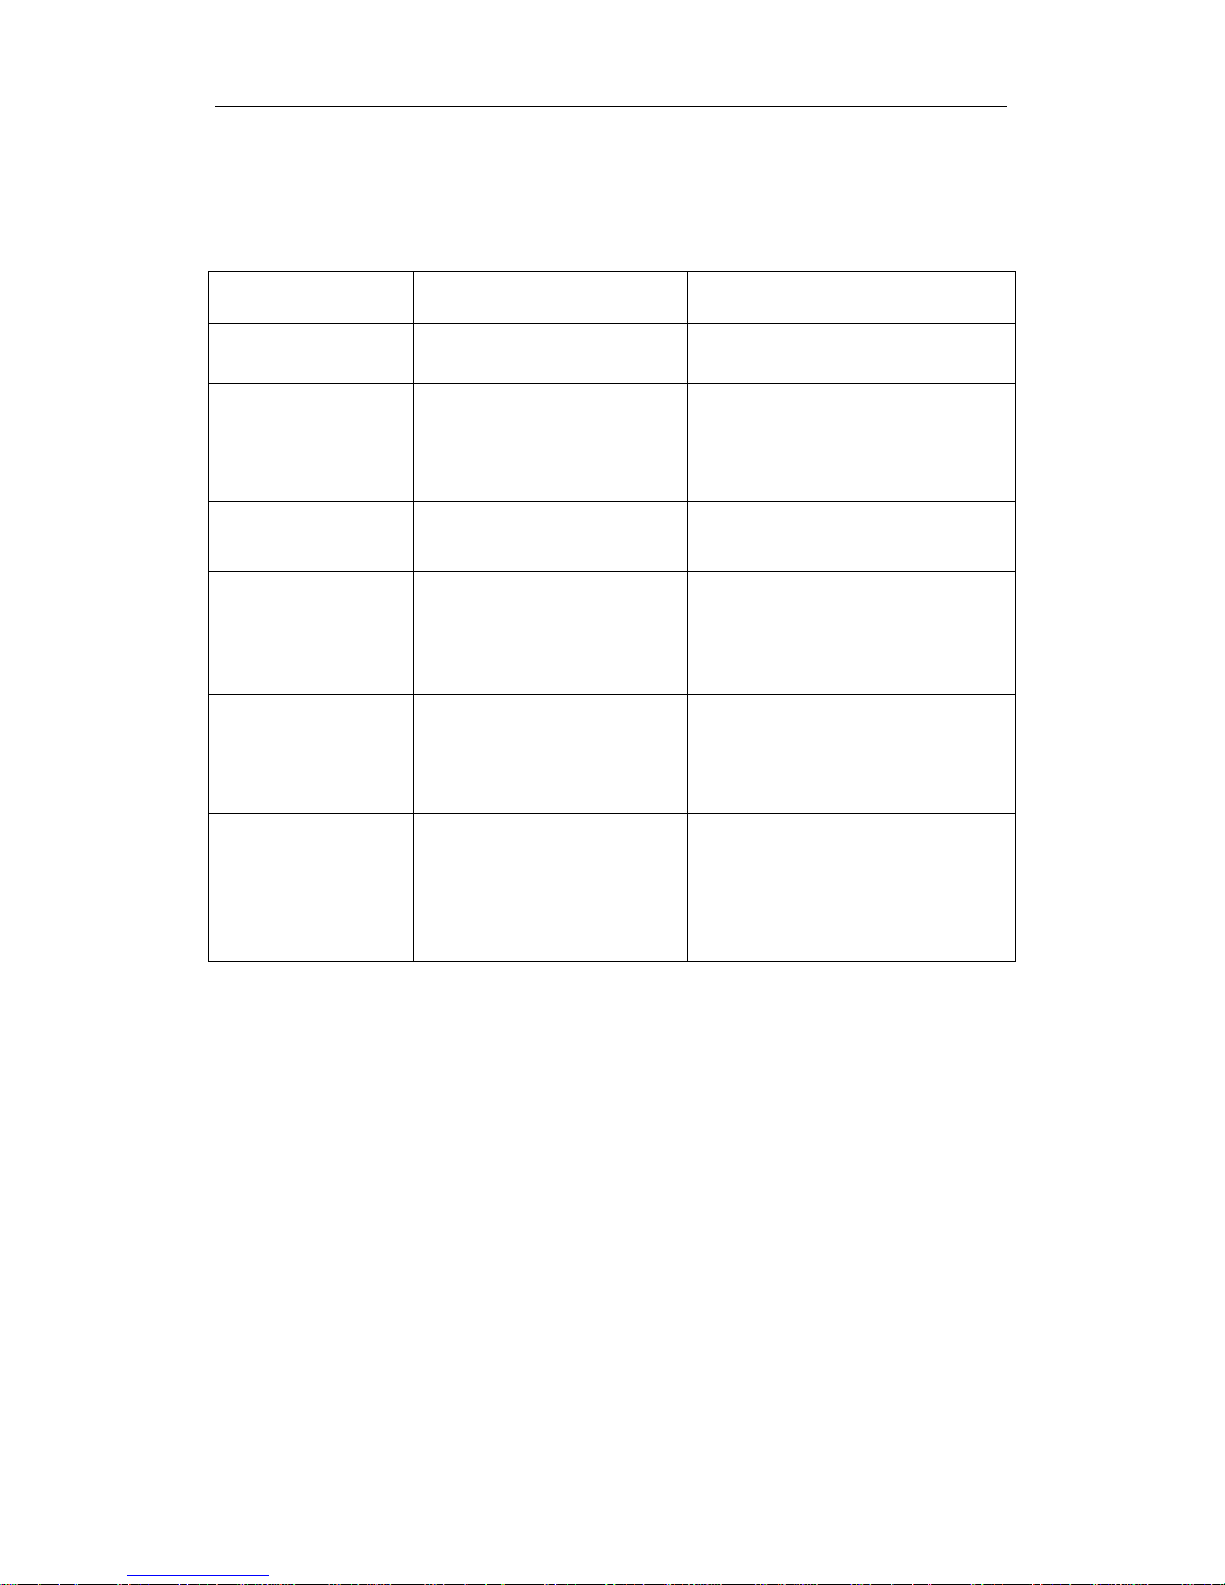
Appendix Trouble shooting
Problems
Reasons
Solutions
All LEDs are off when
power on the switch
Power cord connection error or
power supply failure
Check power cord connection and the
power socket.
The LINK LED is unlit.
1.Network cable is damaged or
the connection is not firm.
2.Wrong network cable type or
the cable is longer than 100m.
Change the network cable.
Slower data transmitting
and packets loss.
The communication pattern of
switch and PDs are not matched.
Changed to matched pattern or configure
to auto-negotiation pattern.
The network cable
works in one
port ,doesn’t work in
another new port.
There is no data transmitting from
PD and the switch can’t learn a
new address to do
communication.
Waiting for 120s, the swith will get
auto-updated address or transmitting
data from the PD, the switch will get
address then.
All the “ACT” LEDs flash
and the network rate
slow down
Caused by broadcast storm.
1. Check if there is a loop problem,
reasonably configure the network.
2. Check if there are large numbers of
broadcast packets from specific sites.
Stop to work after
working for a while.
1. Abnormal power supply.
2. Overheating.
1. Check power connection and the
working voltage;
2. Check the working
environment,including air hole and
switch fan.
 Loading...