

Page 1
AEP NACpoint™
AEP NACpoint
Identity-based Network Admission Control Point
AEP NACpoint is a policy-centric Network Admission Control (NAC) appliance designed to secure LAN and wireless-based networks. NACpoint
provides endpoint vulnerability assessment, user authentication, device quarantine and remediation for your entire network including:
Managed end users
•
Guest access
•
Partner access
•
NACpoint allows you to:
Provide isolated guest access while keeping the corporate network safe
•
Protect network resources against unmanaged devices infected by other less-secure networks
•
Guide end users through self-remediation before vulnerabilities spread
•
Deploy highly granular access policies - with customizable templates - for quick and automatic enforcement
•
Get up and running seamlessly - does not alter existing network congurations or equipment
•
Integrate with all leading vendor infrastructure
•
Conference rooms
•
Mobile users
•
Shared workspaces
•
AEP NACpoint provides a comprehensive data reporting system designed to give insight into:
End user and device vulnerabilities: OS patches, security product version, malware
•
Rogue devices connecting to the network
•
Compliance auditing for policy infractions, authentication and user systems access
•
AEP Networks offers two platforms (AEP NACpoint and AEP NACpoint Small Ofce) that deliver a cost-effective NAC solution regardless of your
organization’s size. The AEP NACpoint Small Ofce platform is ideal as an entry level solution or for small businesses, branch/remote ofces,
or multiple retail locations.
NACpoint is part of a comprehensive AEP Policy Networking security product suite
Features
Granular Policy Engine Powerful, highly customizable enforcement based on device health,
Agentless or Optional Native Agent for vulnerability scans Fast pre- and post-connect assessment of AntiVirus, Firewall, OS, Anti-spyware,
Multiple Automatic Quarantine Zones Isolates infected users for remediation, controlling potential outbreaks from
Identity-based network segmentation Separates resources based on user authentication for policy conformance and
Automatic Vulnerability Updates (via AEP NOCsets) Daily updates of vulnerability knowledge ensures administrators are always
Out-of-band operation Simplied deployment with minimum network interruption. Operates out of
Network Flexibility Integrates with virtually any Layer 2 or Layer 3 managed switch or WAP to
Detailed, Integrated Reporting Engine with Learning Mode Demonstrates immediate value by discovering and auditing any device on the
Benets
•
authentication, location, time of day, Intrusion Prevention System (IPS)
output, Operating System, agent presence, or registry conguration
•
registry and OS patch levels without ANY additional host software
•
spreading
•
control
•
checking against the latest known threats
•
the packet path to maximize security without throughput bottlenecks
•
isolate offending ports. 802.1x network congurations are supported but not
required for full operation
•
network. Comprehensive executive and detailed reports identify vulnerable
users and remediation history. Customizable e-mail alerting on virtually any
policy condition or event for integration into automated IT systems
Page 2
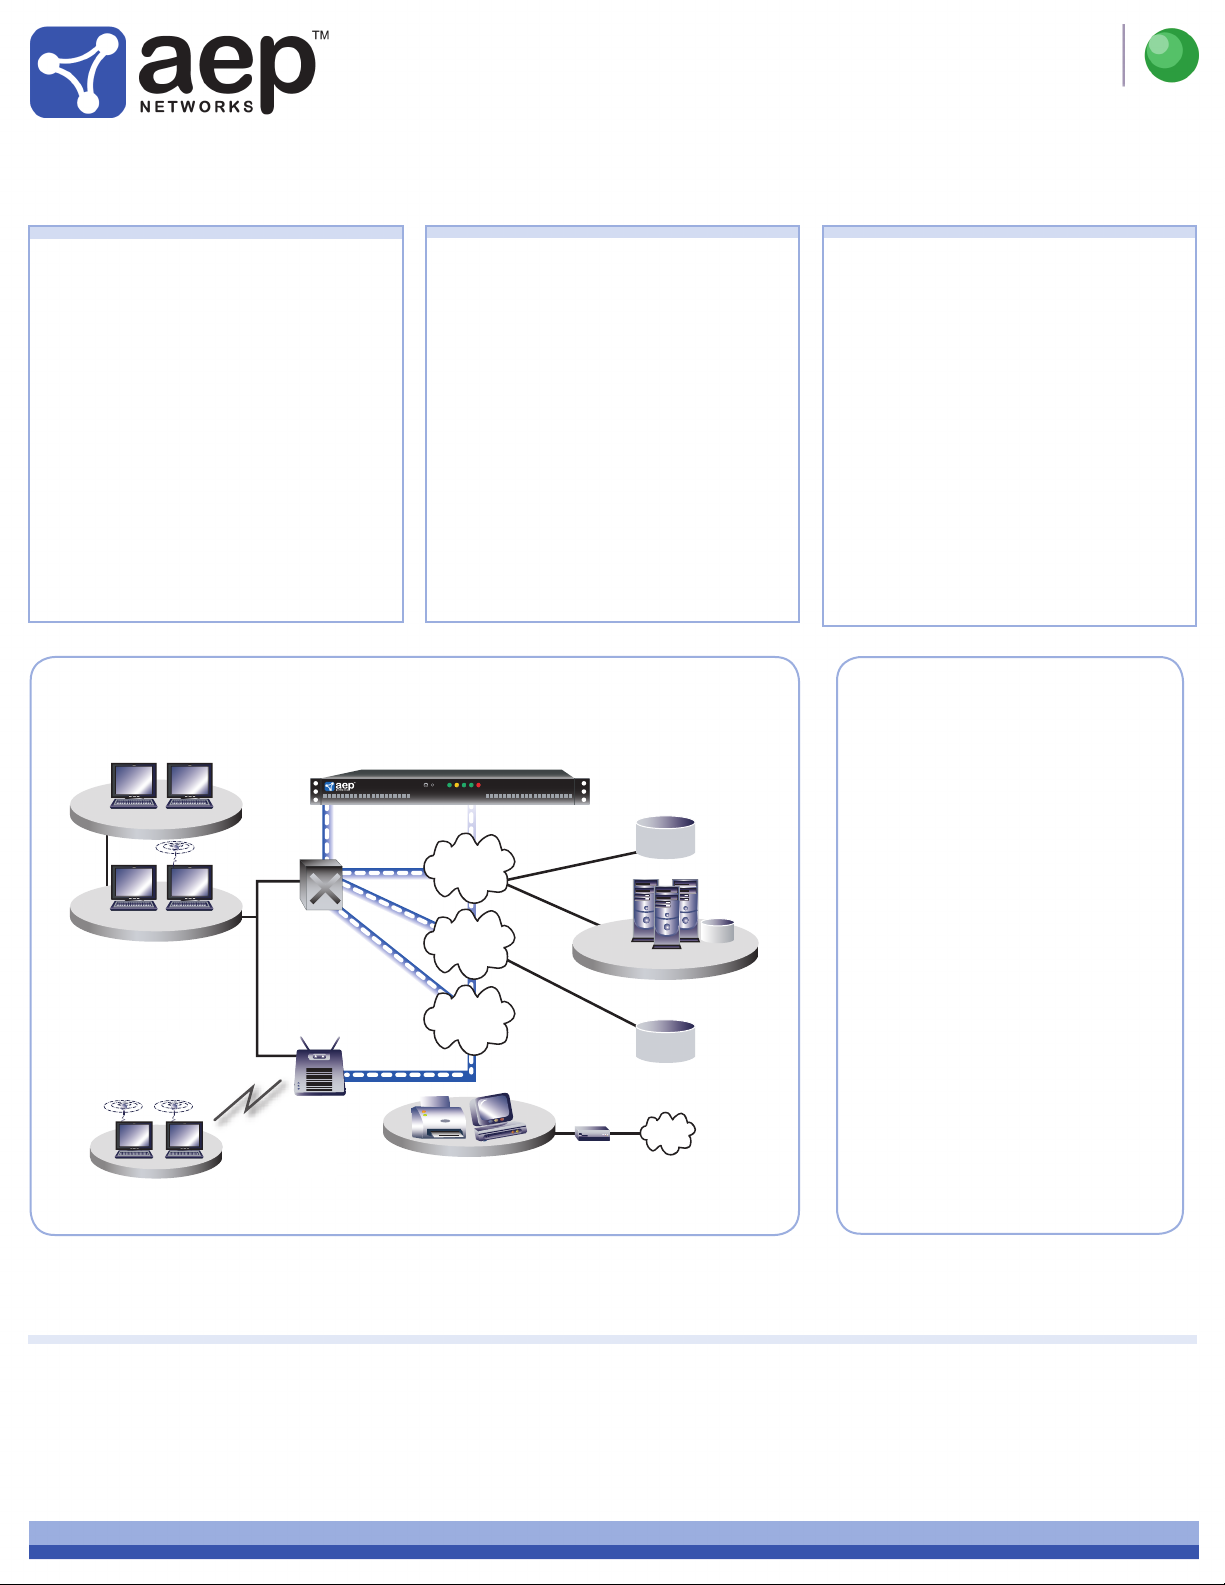
Specications
Internet
Applications
DHCP
Patches
Router
Conference Room
Guest Access
Cisco
Switch
AEP NACpoint™
O
n
/
O
f
f
R
e
s
e
t
P
o
w
e
r
HD
D
E
t
h
o
E
t
h
1
Al
e
r
t
Wireless
Access
Conference Room
Access
Guest/Internet
LAN
Cisco
Aironet
Production
VLAN
Quarantine
VLAN
Hold
VLAN
AEP NACpoint™
Authentication
802.1x
•
Windows® ActiveDirectory Authentication
•
LDAP
•
RADIUS
•
Web login
•
Supported Operating Systems (Client Agent)
Microsoft Windows® XP, Vista
•
Mac OS® X
•
Others (without client agent)
•
Platforms
AEP NACpoint Small Ofce: 50 managed ports
•
(maximum)
AEP NACpoint: 100 managed ports (initial
•
conguration), with expansion capability to
2500+ managed ports
High-Availability active-standby conguration
•
Architecture
Physical Specications
Dimensions: 16.8 in. x 14 in. x 1.7 in. (427 mm
•
x 356 mm x 43 mm)
Fits in a standard single-unit 1U rack
•
Power Requirements
AC Voltage: 100-240 V, 50-60Hz
•
Power Consumption: 500 watts max
•
Port Specications
Two RJ-45 10/100/1000 Ethernet
•
One serial console port
•
Sample Switch and WAP Support
®
3Com
•
•
•
•
•
•
•
•
•
•
•
•
•
•
®
Alcatel
®
Cisco
Enterasys
Extreme
Foundry
HP ProCurve
Nortel
Allied Telesis
Hitachi
Trapeze
Aruba
Meru
®
®
®
®
®
®
®
®
And more!
®
ABOUT AEP NETWORKS
AEP Networks offers a comprehensive
Policy Networking solution that
provides complete security starting
at the endpoints and working
throughout a network – from the edge
to the core. AEP’s integrated portfolio
of security products includes network
admission control enforcement
points, identity-based application
security gateways, SSL VPNs,
high assurance IPSec-based VPN
encryptors, and hardware security
modules for key management. Our
products address the most demanding
security requirements of publicsector organizations and commercial
enterprises internationally. The
company is headquartered in
Somerset, New Jersey, with ofces
worldwide.
Contact Us
CORPORATE HEADQUARTERS
347 ELIZABETH AVE., SUITE 100
SOMERSET NJ 08873
TOLL-FREE: 1 877 638 4552
TEL: (+1) 732 652 5200
© 2007 AEP Networks, Inc. All rights reserved. AEP Networks, the AEP Networks logo, and NACpoint are trademarks of AEP Networks,
Inc., with registration pending in the United States. Netilla, SmartGate, SmartPass and SmartAdmin are registered trademarks of AEP
Networks, Inc. All other trademarks or registered trademarks contained herein are the property of their respective owners.
EUROPE
FOCUS 31, WEST WING
CLEVELAND ROAD
HEMEL HEMPSTEAD
HERTS HP2 7BW U.K.
TEL: (+44) 1442 458 600
GREATER CHINA
(MAINLAND, TAIWAN, HONG KONG)
SHANGHAI, CHINA
TEL: (+86) 136 4626 0288
JAPAN, SOUTHEAST ASIA, AUSTRALIA, NEW ZEALAND
JOYO BLDG 6-22-6
SHIMBASHI MINATO-KU
TOKYO 105-0004
JAPAN
TEL: (+81) 3 3432 3336
www.aepnetworks.com
 Loading...